Submitted URL:
http://www.revouninstaller.com/free-install-thankyou/ 9yr old
Effective URL:
https://www.revouninstaller.com/free-install-thankyou/ 9yr old
Submission: On May 15 via manual (May 15th 2025, 10:03:08 am UTC) from PT — Scanned from PT

Summary

This website contacted 28 IPs in 3 countries across 23 domains to perform 79 HTTP transactions. The main IP is 146.20.152.114, located in United States and belongs to RACKSPACE, US. The main domain is www.revouninstaller.com. The Cisco Umbrella rank of the primary domain is 187357. 9yr old
TLS certificate: Issued by DigiCert EV RSA CA G2 on April 14th 2025. Valid for: 1yr.
This is the only time www.revouninstaller.com was scanned on urlscan.io!

urlscan.io Verdict: No classification

Domain & IP information

IP Address AS Autonomous System
7 146.20.152.114 146.20.152.114 27357 (RACKSPACE) (RACKSPACE)
2 104.18.10.207 104.18.10.207 13335 (CLOUDFLAR...) (CLOUDFLARENET)
12 169.150.247.36 169.150.247.36 60068 (CDN77 Dat...) (CDN77 Datacamp Limited)
1 52.222.236.71 52.222.236.71 16509 (AMAZON-02) (AMAZON-02)
3 104.22.69.95 104.22.69.95 13335 (CLOUDFLAR...) (CLOUDFLARENET)
12 23.57.20.115 23.57.20.115 16625 (AKAMAI-AS) (AKAMAI-AS)
1 34.96.102.8 34.96.102.8 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM)
7 216.198.54.3 216.198.54.3 209242 (CLOUDFLAR...) (CLOUDFLARESPECTRUM Cloudflare London)
1 142.250.185.234 142.250.185.234 15169 (GOOGLE) (GOOGLE)
1 104.16.174.226 104.16.174.226 13335 (CLOUDFLAR...) (CLOUDFLARENET)
3 142.250.186.72 142.250.186.72 15169 (GOOGLE) (GOOGLE)
3 142.250.184.202 142.250.184.202 15169 (GOOGLE) (GOOGLE)
5 52.222.236.107 52.222.236.107 16509 (AMAZON-02) (AMAZON-02)
3 216.58.206.35 216.58.206.35 15169 (GOOGLE) (GOOGLE)
1 169.150.247.38 169.150.247.38 60068 (CDN77 Dat...) (CDN77 Datacamp Limited)
1 142.250.186.100 142.250.186.100 15169 (GOOGLE) (GOOGLE)
2 216.239.38.178 216.239.38.178 15169 (GOOGLE) (GOOGLE)
2 157.240.252.13 157.240.252.13 32934 (FACEBOOK) (FACEBOOK)
1 146.75.116.157 146.75.116.157 54113 (FASTLY) (FASTLY)
1 162.159.140.229 162.159.140.229 13335 (CLOUDFLAR...) (CLOUDFLARENET)
1 172.66.0.227 172.66.0.227 13335 (CLOUDFLAR...) (CLOUDFLARENET)
1 216.198.54.1 216.198.54.1 209242 (CLOUDFLAR...) (CLOUDFLARESPECTRUM Cloudflare London)
3 157.240.252.35 157.240.252.35 32934 (FACEBOOK) (FACEBOOK)
1 104.16.200.19 104.16.200.19 13335 (CLOUDFLAR...) (CLOUDFLARENET)
2 216.239.34.36 216.239.34.36 15169 (GOOGLE) (GOOGLE)
1 142.251.168.154 142.251.168.154 15169 (GOOGLE) (GOOGLE)
1 142.250.181.227 142.250.181.227 15169 (GOOGLE) (GOOGLE)
79 28
Apex Domain
Subdomains
Transfer
13 cookiefirst.com
consent.cookiefirst.com — Cisco Umbrella Rank: 40643 7yr old
edge.cookiefirst.com — Cisco Umbrella Rank: 50538 5yr old
91 KB
12 rackcdn.com
f057a20f961f56a72089-b74530d2d26278124f446233f95622ef.ssl.cf1.rackcdn.com — Cisco Umbrella Rank: 956036 8yr old
477 KB
7 zdassets.com
static.zdassets.com — Cisco Umbrella Rank: 4198 9yr old
ekr.zdassets.com — Cisco Umbrella Rank: 5078 9yr old
345 KB
7 revouninstaller.com
www.revouninstaller.com — Cisco Umbrella Rank: 187357 9yr old
77 KB
6 trustpilot.com
widget.trustpilot.com — Cisco Umbrella Rank: 6565 10yr old
28 KB
4 googleapis.com
ajax.googleapis.com — Cisco Umbrella Rank: 746 10yr old
fonts.googleapis.com — Cisco Umbrella Rank: 129 10yr old
35 KB
3 facebook.com
www.facebook.com — Cisco Umbrella Rank: 140 11yr old
219 B
3 google.com
www.google.com — Cisco Umbrella Rank: 9 13yr old
region1.analytics.google.com — Cisco Umbrella Rank: 3431 5yr old
3 gstatic.com
fonts.gstatic.com 10yr old
90 KB
3 googletagmanager.com
www.googletagmanager.com — Cisco Umbrella Rank: 122 13yr old
286 KB
3 elfsight.com
static.elfsight.com — Cisco Umbrella Rank: 19819 7yr old
core.service.elfsight.com — Cisco Umbrella Rank: 21546 5yr old
299 KB
2 facebook.net
connect.facebook.net — Cisco Umbrella Rank: 271 13yr old
84 KB
2 google-analytics.com
www.google-analytics.com — Cisco Umbrella Rank: 133 13yr old
22 KB
2 bootstrapcdn.com
stackpath.bootstrapcdn.com — Cisco Umbrella Rank: 4950 8yr old
41 KB
1 google.pt
www.google.pt — Cisco Umbrella Rank: 20374 10yr old
408 B
1 doubleclick.net
stats.g.doubleclick.net — Cisco Umbrella Rank: 308 10yr old
563 B
1 zopim.io
v2assets.zopim.io — Cisco Umbrella Rank: 104720 10yr old
18 KB
1 zendesk.com
vsrevogroup.zendesk.com 8yr old
1 KB
1 twitter.com
analytics.twitter.com — Cisco Umbrella Rank: 1421 10yr old
667 B
1 t.co
t.co — Cisco Umbrella Rank: 1243 13yr old
645 B
1 ads-twitter.com
static.ads-twitter.com — Cisco Umbrella Rank: 1540 10yr old
16 KB
1 jsdelivr.net
cdn.jsdelivr.net — Cisco Umbrella Rank: 412 13yr old
8 KB
1 mailjet.com
app.mailjet.com — Cisco Umbrella Rank: 238103 9yr old
8 KB
79 23
Domain Requested by
12 f057a20f961f56a72089-b74530d2d26278124f446233f95622ef.ssl.cf1.rackcdn.com www.revouninstaller.com
12 consent.cookiefirst.com www.revouninstaller.com
consent.cookiefirst.com
7 www.revouninstaller.com www.revouninstaller.com
6 static.zdassets.com www.revouninstaller.com
static.zdassets.com
6 widget.trustpilot.com www.revouninstaller.com
widget.trustpilot.com
3 www.facebook.com connect.facebook.net
www.revouninstaller.com
3 fonts.gstatic.com fonts.googleapis.com
3 fonts.googleapis.com www.revouninstaller.com
static.elfsight.com
3 www.googletagmanager.com www.revouninstaller.com
www.googletagmanager.com
2 region1.analytics.google.com www.googletagmanager.com
2 connect.facebook.net www.revouninstaller.com
connect.facebook.net
2 www.google-analytics.com www.googletagmanager.com
www.google-analytics.com
2 static.elfsight.com www.revouninstaller.com
static.elfsight.com
2 stackpath.bootstrapcdn.com www.revouninstaller.com
1 www.google.pt
1 stats.g.doubleclick.net www.googletagmanager.com
1 v2assets.zopim.io
1 vsrevogroup.zendesk.com static.zdassets.com
1 analytics.twitter.com www.revouninstaller.com
1 t.co www.revouninstaller.com
1 static.ads-twitter.com www.revouninstaller.com
1 www.google.com www.googletagmanager.com
1 edge.cookiefirst.com consent.cookiefirst.com
1 core.service.elfsight.com static.elfsight.com
1 ekr.zdassets.com static.zdassets.com
1 cdn.jsdelivr.net www.revouninstaller.com
1 ajax.googleapis.com www.revouninstaller.com
1 app.mailjet.com www.revouninstaller.com
79 28
Subject Issuer Validity Valid
www.revouninstaller.com
DigiCert EV RSA CA G2
2025-04-14 -
2026-05-15
1yr crt.sh
bootstrapcdn.com
WE1
2025-05-14 -
2025-08-12
3mo crt.sh
*.cookiefirst.com
Sectigo RSA Domain Validation Secure Server CA
2024-12-03 -
2025-12-16
1yr crt.sh
*.trustpilot.com
Amazon RSA 2048 M02
2024-12-03 -
2026-01-01
1yr crt.sh
static.elfsight.com
WE1
2025-05-14 -
2025-08-12
3mo crt.sh
*.ssl.cf1.rackcdn.com
DigiCert TLS RSA SHA256 2020 CA1
2025-01-24 -
2026-01-26
1yr crt.sh
mailjet.com
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2025-03-17 -
2026-04-15
1yr crt.sh
zdassets.com
WE1
2025-04-29 -
2025-07-28
3mo crt.sh
upload.video.google.com
WE2
2025-04-21 -
2025-07-14
3mo crt.sh
*.jsdelivr.net
Sectigo RSA Domain Validation Secure Server CA
2025-04-25 -
2026-05-04
1yr crt.sh
*.google-analytics.com
WE2
2025-04-21 -
2025-07-14
3mo crt.sh
*.gstatic.com
WE2
2025-04-21 -
2025-07-14
3mo crt.sh
elfsight.com
WE1
2025-04-01 -
2025-06-30
3mo crt.sh
edge.cookiefirst.com
R10
2025-05-06 -
2025-08-04
3mo crt.sh
*.google.com
WE2
2025-04-21 -
2025-07-14
3mo crt.sh
*.facebook.com
DigiCert SHA2 High Assurance Server CA
2025-02-21 -
2025-05-22
3mo crt.sh
ads-twitter.com
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2024-06-25 -
2025-06-24
1yr crt.sh
t.co
E6
2025-03-24 -
2025-06-22
3mo crt.sh
twitter.com
E6
2025-05-01 -
2025-07-30
3mo crt.sh
vsrevogroup.zendesk.com
E5
2025-05-13 -
2025-08-11
3mo crt.sh
zopim.io
WE1
2025-03-21 -
2025-06-19
3mo crt.sh
*.g.doubleclick.net
WR2
2025-04-21 -
2025-07-14
3mo crt.sh
*.google.pt
WE2
2025-04-21 -
2025-07-14
3mo crt.sh

This page contains 5 frames:

Primary Page: https://www.revouninstaller.com/free-install-thankyou/
Frame ID: 5103554369EABF25A6CF3819DE14C4A4
Requests: 91 HTTP requests in this frame

Frame: https://widget.trustpilot.com/trustboxes/5419b6a8b0d04a076446a9ad/index.html?templateId=5419b6a8b0d04a076446a9ad&businessunitId=600037798b18380001bcf594
Frame ID: EBB583316825EB057EF94223C7FE7AF4
Requests: 5 HTTP requests in this frame

Frame: https://www.googletagmanager.com/static/service_worker/5570/sw_iframe.html?origin=https%3A%2F%2Fwww.revouninstaller.com
Frame ID: 641268CD15F2F0B15419A8F37E3A7391
Requests: 1 HTTP requests in this frame

Frame: https://static.zdassets.com/web_widget/classic/latest/web-widget-main-4138c17.js
Frame ID: 65CC6926C4F77FED3F82EE4AF9051873
Requests: 6 HTTP requests in this frame

Frame: https://v2assets.zopim.io/393O9gB158xzzs9O82F04ypD5NUqTehW-banner?1654172833774
Frame ID: 9B2F90C89DB641BC27655D5032240EFA
Requests: 1 HTTP requests in this frame

Screenshot

Page Title

Thank you for installing Revo Uninstaller Free

Page URL History Show full URLs

  1. http://www.revouninstaller.com/free-install-thankyou/ HTTP 307
    https://www.revouninstaller.com/free-install-thankyou/ Page URL

Detected technologies

(CMS)
Overall confidence: 100%
Detected patterns
  • <link rel=["']stylesheet["'] [^>]+/wp-(?:content|includes)/
  • /wp-(?:content|includes)/

(UI frameworks)
Overall confidence: 100%
Detected patterns
  • <link[^>]* href=[^>]*?bootstrap(?:[^>]*?([0-9a-fA-F]{7,40}|[\d]+(?:.[\d]+(?:.[\d]+)?)?)|)[^>]*?(?:\.min)?\.css
  • bootstrap(?:[^>]*?([0-9a-fA-F]{7,40}|[\d]+(?:.[\d]+(?:.[\d]+)?)?)|)[^>]*?(?:\.min)?\.js

(Widgets)
Overall confidence: 100%
Detected patterns
  • //connect\.facebook\.([a-z]+)/[^/]*/[a-z]*\.js

(Analytics)
Overall confidence: 100%
Detected patterns
  • google-analytics\.com/(?:ga|urchin|analytics)\.js

(Font scripts)
Overall confidence: 100%
Detected patterns
  • <link[^>]* href=[^>]+fonts\.(?:googleapis|google)\.com

(Tag managers)
Overall confidence: 100%
Detected patterns
  • googletagmanager\.com/ns\.html[^>]+></iframe>
  • googletagmanager\.com/gtm\.js
  • googletagmanager\.com/gtag/js

(JavaScript libraries)
Overall confidence: 100%
Detected patterns
  • /([\d.]+)/jquery(?:\.min)?\.js
  • jquery.*\.js(?:\?ver(?:sion)?=([\d.]+))?

(CDN)
Overall confidence: 100%
Detected patterns
  • //cdn\.jsdelivr\.net/

Page Statistics

79
Requests

100 %
HTTPS

0 %
IPv6

23
Domains

28
Subdomains

28
IPs

3
Countries

1928 kB
Transfer

5162 kB
Size

17
Cookies

Page URL History

This captures the URL locations of the websites, including HTTP redirects and client-side redirects via JavaScript or Meta fields.

  1. http://www.revouninstaller.com/free-install-thankyou/ HTTP 307
    https://www.revouninstaller.com/free-install-thankyou/ Page URL

Redirected requests

There were HTTP redirect chains for the following requests:

79 HTTP transactions
25 data transactions

Method
Protocol
Status Resource
Path
Size
x-fer
Time
Latency
Type
MIME-Type
IP
Location
GET
H2
200
Primary Request / Show response
www.revouninstaller.com/free-install-thankyou/
Redirect Chain
  • http://www.revouninstaller.com/free-install-thankyou/
  • https://www.revouninstaller.com/free-install-thankyou/
77 KB
18 KB
736ms
366ms
Document
text/html
146.20.152.114
RACKSPACE
General
Full URL
https://www.revouninstaller.com/free-install-thankyou/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
146.20.152.114 , United States, ASN27357 (RACKSPACE, US),
Reverse DNS
1333686-web1.vsrevogroup.com
Software
XYZ /
Resource Hash
6e9fa14c90e4d77cb1490ba8c8437c87e8a624ebebb6c09ab8fb0b86fd50163d
Security Headers
Name Value
Content-Security-Policy frame-ancestors 'self';
Strict-Transport-Security max-age=31536000; includeSubdomains
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 1; mode=block

Request headers

Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36

Response headers

cache-control
private, proxy-revalidate, s-maxage=0 max-age=0, private, no-store, no-cache, must-revalidate
cf-edge-cache
no-cache
content-encoding
gzip
content-length
18093
content-security-policy
frame-ancestors 'self';
content-type
text/html; charset=UTF-8
date
Thu, 15 May 2025 10:03:08 GMT
expires
Thu, 19 Nov 1981 08:52:00 GMT
link
<https://www.revouninstaller.com/?p=3836>; rel=shortlink
permissions-policy
interest-cohort=()
pragma
no-cache
referrer-policy
no-referrer, strict-origin-when-cross-origin
server
XYZ
strict-transport-security
max-age=31536000; includeSubdomains
vary
Accept-Encoding
x-content-type-options
nosniff
x-frame-options
SAMEORIGIN
x-permitted-cross-domain-policies
none
x-xss-protection
1; mode=block

Redirect headers

Location
https://www.revouninstaller.com/free-install-thankyou/
Non-Authoritative-Reason
HttpsUpgrades
GET
H2
200
cookiefirst-plugin-public.css
www.revouninstaller.com/wp-content/plugins/cookiefirst-plugin/public/css/
98 B
225 B
144ms
142ms
Stylesheet
text/css
146.20.152.114
RACKSPACE
General
Full URL
https://www.revouninstaller.com/wp-content/plugins/cookiefirst-plugin/public/css/cookiefirst-plugin-public.css?ver=1.0.0
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
146.20.152.114 , United States, ASN27357 (RACKSPACE, US),
Reverse DNS
1333686-web1.vsrevogroup.com
Software
XYZ /
Resource Hash
547dda3c14b284819be511be1e410da94a5efc6ccc4a9afe1c75394f9333191a
Security Headers
Name Value
Content-Security-Policy frame-ancestors 'self';
Strict-Transport-Security max-age=31536000; includeSubdomains
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 1; mode=block

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/free-install-thankyou/

Response headers

content-encoding
gzip
x-permitted-cross-domain-policies
none
x-content-type-options
nosniff
expires
max-age=A10368000, public
date
Thu, 15 May 2025 10:03:09 GMT
last-modified
Thu, 09 May 2024 06:23:47 GMT
vary
Accept-Encoding
content-type
text/css
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=31536000; includeSubdomains
content-security-policy
frame-ancestors 'self';
cache-control
max-age=0, private, no-store, no-cache, must-revalidate
referrer-policy
no-referrer, strict-origin-when-cross-origin
permissions-policy
interest-cohort=()
accept-ranges
bytes
content-length
106
x-xss-protection
1; mode=block
server
XYZ
GET
H3
200
bootstrap.min.css
stackpath.bootstrapcdn.com/bootstrap/4.4.1/css/
156 KB
25 KB
109ms
55ms
Stylesheet
text/css
104.18.10.207
CLOUDFLARENET
General
Full URL
https://stackpath.bootstrapcdn.com/bootstrap/4.4.1/css/bootstrap.min.css?ver=4.4.1
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.18.10.207 -, , ASN13335 (CLOUDFLARENET, US),
Reverse DNS
Software
cloudflare /
Resource Hash
2ff5b959fa9f6b4b1d04d20a37d706e90039176ab1e2a202994d9580baeebfd6
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

cdn-status
200
content-encoding
br
cf-cache-status
HIT
etag
"7cc40c199d128af6b01e74a28c5900b0"
age
1801488
x-content-type-options
nosniff
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Thu, 15 May 2025 10:03:09 GMT
last-modified
Mon, 25 Jan 2021 22:04:09 GMT
content-type
text/css; charset=utf-8
vary
Accept-Encoding
cdn-cache
HIT
cdn-cachedat
11/18/2024 10:38:05
cdn-requestpullcode
200
priority
u=0,i=?0
strict-transport-security
max-age=31536000; includeSubDomains; preload
cache-control
public, max-age=31919000
cdn-requestpullsuccess
True
timing-allow-origin
*
cdn-requesttime
0
cdn-uid
b1941f61-b576-4f40-80de-5677acb38f74
cdn-requestid
54f4579b2875fcf09191ec1e20784cff
cross-origin-resource-policy
cross-origin
cdn-pullzone
252412
cdn-proxyver
1.07
cf-ray
9401cdc6e89e6932-LIS
access-control-allow-origin
*
cdn-edgestorageid
1216
server
cloudflare
cdn-requestcountrycode
FR
GET
H2
200
autoptimize_single_43c6b5a3c1ca4c32d1940a3f2aaba505.css
www.revouninstaller.com/wp-content/cache/autoptimize/css/
72 KB
16 KB
162ms
161ms
Stylesheet
text/css
146.20.152.114
RACKSPACE
General
Full URL
https://www.revouninstaller.com/wp-content/cache/autoptimize/css/autoptimize_single_43c6b5a3c1ca4c32d1940a3f2aaba505.css?ver=1.1
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
146.20.152.114 , United States, ASN27357 (RACKSPACE, US),
Reverse DNS
1333686-web1.vsrevogroup.com
Software
XYZ /
Resource Hash
f2cbf1df88192121c656a71c19c615162f06366cd47947dc552550880e6094e4
Security Headers
Name Value
Content-Security-Policy frame-ancestors 'self';
Strict-Transport-Security max-age=31536000; includeSubdomains
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 1; mode=block

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/free-install-thankyou/

Response headers

content-encoding
gzip
x-permitted-cross-domain-policies
none
x-content-type-options
nosniff
expires
max-age=A10368000, public
date
Thu, 15 May 2025 10:03:09 GMT
last-modified
Thu, 15 May 2025 09:54:42 GMT
vary
Accept-Encoding
content-type
text/css
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=31536000; includeSubdomains
content-security-policy
frame-ancestors 'self';
cache-control
max-age=0, private, no-store, no-cache, must-revalidate
referrer-policy
no-referrer, strict-origin-when-cross-origin
permissions-policy
interest-cohort=()
accept-ranges
bytes
content-length
16011
x-xss-protection
1; mode=block
server
XYZ
GET
H2
200
jquery.min.js Show response
www.revouninstaller.com/wp-includes/js/jquery/
86 KB
30 KB
244ms
242ms
Script
application/javascript
146.20.152.114
RACKSPACE
General
Full URL
https://www.revouninstaller.com/wp-includes/js/jquery/jquery.min.js?ver=3.7.1
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
146.20.152.114 , United States, ASN27357 (RACKSPACE, US),
Reverse DNS
1333686-web1.vsrevogroup.com
Software
XYZ /
Resource Hash
cb6f2d32c49d1c2b25e9ffc9aaafa3f83075346c01bcd4ae6eb187392a4292cf
Security Headers
Name Value
Content-Security-Policy frame-ancestors 'self';
Strict-Transport-Security max-age=31536000; includeSubdomains
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 1; mode=block

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/free-install-thankyou/

Response headers

content-encoding
gzip
x-permitted-cross-domain-policies
none
x-content-type-options
nosniff
expires
max-age=A10368000, public
date
Thu, 15 May 2025 10:03:09 GMT
last-modified
Mon, 20 Nov 2023 05:50:37 GMT
vary
Accept-Encoding
content-type
application/javascript
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=31536000; includeSubdomains
content-security-policy
frame-ancestors 'self';
cache-control
max-age=0, private, no-store, no-cache, must-revalidate
referrer-policy
no-referrer, strict-origin-when-cross-origin
permissions-policy
interest-cohort=()
accept-ranges
bytes
content-length
30368
x-xss-protection
1; mode=block
server
XYZ
GET
H2
200
consent.js Show response
consent.cookiefirst.com/sites/revouninstaller.com-eaf2c1f3-7cb1-4b17-9342-3053be0001d7/
6 KB
3 KB
868ms
705ms
Script
application/javascript
169.150.247.36
CDN77 Datacamp Li...
General
Full URL
https://consent.cookiefirst.com/sites/revouninstaller.com-eaf2c1f3-7cb1-4b17-9342-3053be0001d7/consent.js?ver=025bcaeb072a0ece6e6e557f241bd7bd
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
169.150.247.36 Frankfurt am Main, Germany, ASN60068 (CDN77 Datacamp Limited, GB),
Reverse DNS
169-150-247-36.bunnyinfra.net
Software
Cookie First CDN-DE1-1079 /
Resource Hash
4288b1e018ceffbce943fa7d4664ea4e8e9f1c0395ec549dc8166c7a3b206f87

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

cdn-status
200
access-control-expose-headers
Server, x-goog-meta-frames, Content-Length, Content-Type, Range, X-Requested-With, If-Modified-Since, If-None-Match, visitor-location
content-encoding
zstd
etag
"6815cfc8-1698"
cdn-fileserver
599
date
Thu, 15 May 2025 10:03:10 GMT
cdn-storageserver
DE-587
last-modified
Sat, 03 May 2025 08:11:52 GMT
content-type
application/javascript
vary
Accept-Encoding
cdn-cache
REVALIDATED
access-control-allow-headers
Request-Id, Server, x-goog-meta-frames, Content-Length, Content-Type, Range, X-Requested-With, If-Modified-Since, If-None-Match, traceparent
cdn-requestpullcode
200
cdn-cachedat
05/06/2025 17:50:16
cache-control
public, max-age=30
cdn-requestpullsuccess
True
visitor-location
PT
cdn-requesttime
1
cdn-uid
d602dab6-3f92-4809-a378-608fd2b89403
cdn-requestid
8aefe25ab152f2994933c32e06c72d48
cdn-pullzone
236985
cdn-proxyver
1.27
access-control-allow-origin
*
cdn-edgestorageid
1079
server
Cookie First CDN-DE1-1079
cdn-requestcountrycode
PT
GET
H2
200
tp.widget.bootstrap.min.js Show response
widget.trustpilot.com/bootstrap/v5/
23 KB
8 KB
292ms
90ms
Script
application/x-javascript
52.222.236.71
AMAZON-02
General
Full URL
https://widget.trustpilot.com/bootstrap/v5/tp.widget.bootstrap.min.js
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
52.222.236.71 , United States, ASN16509 (AMAZON-02, US),
Reverse DNS
server-52-222-236-71.fra56.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
c69de41dda83f00cc1b13dba90a57f25df046286ecd227bdd0c4d51d94947b61
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

content-encoding
gzip
etag
"7d4644d89e45fe92623bdd628e60e8dd"
age
35165
x-content-type-options
nosniff
x-cache
Hit from cloudfront
x-amz-cf-id
UwC6QJGZyb4V_tffiokgXT4HX8ESnR1-35EpodVuntac1ODI21AKlQ==
date
Thu, 15 May 2025 00:17:06 GMT
content-type
application/x-javascript
last-modified
Wed, 09 Oct 2024 12:04:38 GMT
strict-transport-security
max-age=31536000
cache-control
max-age=86400
via
1.1 82386e4e4f56a0c01411d1aea6f3fd46.cloudfront.net (CloudFront)
accept-ranges
bytes
content-length
7350
x-xss-protection
1; mode=block
x-amz-cf-pop
FRA56-P4
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H2
200
platform.js Show response
static.elfsight.com/platform/
41 KB
15 KB
254ms
52ms
Script
application/javascript
104.22.69.95
CLOUDFLARENET
General
Full URL
https://static.elfsight.com/platform/platform.js
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.22.69.95 -, , ASN13335 (CLOUDFLARENET, US),
Reverse DNS
Software
cloudflare /
Resource Hash
4148d0c90ebd46c31db6786edc9679893db53c97e68fee894309bdf9913cc9d5
Security Headers
Name Value
Strict-Transport-Security max-age=0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

content-encoding
gzip
cf-cache-status
HIT
etag
W/"73daad4953f9609a9f505ced27eb4b8f"
age
965
alt-svc
h3=":443"; ma=86400
date
Thu, 15 May 2025 10:03:10 GMT
x-rgw-object-type
Normal
content-type
application/javascript
last-modified
Fri, 18 Apr 2025 06:31:10 GMT
vary
Origin, Access-Control-Request-Headers, Access-Control-Request-Method, Accept-Encoding
x-do-cdn-uuid
e32c40dc-02c3-4408-a6ec-51bfedff6dd9
strict-transport-security
max-age=0
cache-control
max-age=3600
speculation-rules
"/cdn-cgi/speculation"
x-amz-request-id
tx000008a9481150cfd68c2-006801f461-f539a60-sfo2b
cf-ray
9401cdcd4ece1df8-LIS
server
cloudflare
GET
H/1.1
200
OK
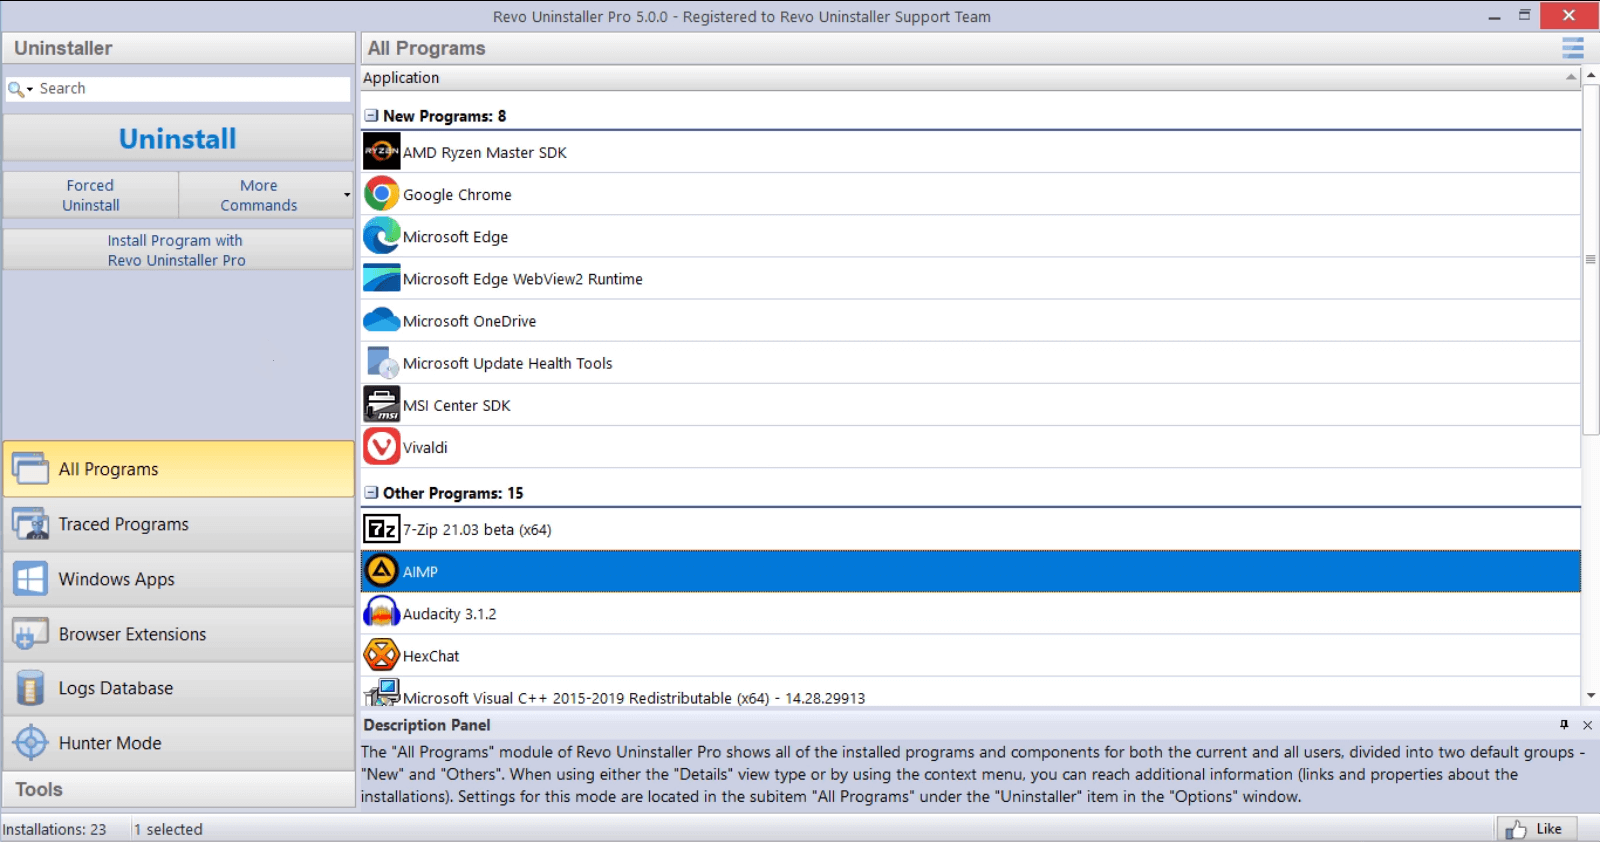
uninstaller.png
f057a20f961f56a72089-b74530d2d26278124f446233f95622ef.ssl.cf1.rackcdn.com/site/screens-5/
115 KB
115 KB
326ms
128ms
Image
image/png
23.57.20.115
AKAMAI-AS
General
Full URL
https://f057a20f961f56a72089-b74530d2d26278124f446233f95622ef.ssl.cf1.rackcdn.com/site/screens-5/uninstaller.png
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_256_GCM
Server
23.57.20.115 Düsseldorf, Germany, ASN16625 (AKAMAI-AS, US),
Reverse DNS
a23-57-20-115.deploy.static.akamaitechnologies.com
Software
/
Resource Hash
568849a9b53202c322377a9061b5f918fd01fffe5e76783afe5d323a1d6400a6

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

Origin
https://mycloud.rackspace.com
Cache-Control
public, max-age=27386169
ETag
c906d9048e7fd55333ed12d888b634e2
X-Timestamp
1652081058.19629
Connection
keep-alive
Expires
Sat, 28 Mar 2026 09:19:18 GMT
Accept-Ranges
bytes
X-Trans-Id
txff094752bb2646138bb99-00651d72d1dfw1
Content-Length
117465
Date
Thu, 15 May 2025 10:03:09 GMT
Last-Modified
Mon, 09 May 2022 07:24:19 GMT
Content-Type
image/png
GET
H/1.1
200
OK
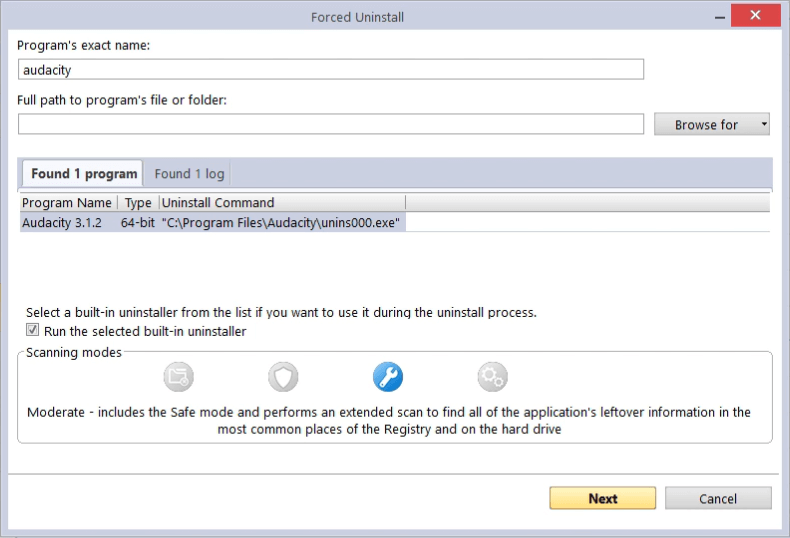
forced-uninstall.png
f057a20f961f56a72089-b74530d2d26278124f446233f95622ef.ssl.cf1.rackcdn.com/site/screens-5/
43 KB
44 KB
317ms
119ms
Image
image/png
23.57.20.115
AKAMAI-AS
General
Full URL
https://f057a20f961f56a72089-b74530d2d26278124f446233f95622ef.ssl.cf1.rackcdn.com/site/screens-5/forced-uninstall.png
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_256_GCM
Server
23.57.20.115 Düsseldorf, Germany, ASN16625 (AKAMAI-AS, US),
Reverse DNS
a23-57-20-115.deploy.static.akamaitechnologies.com
Software
/
Resource Hash
4302eac6f74fb5f3ff2229402ddb0bef9a518f8188319428d157159768fa2366

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

Origin
https://mycloud.rackspace.com
Cache-Control
public, max-age=27449920
ETag
7f4bffffbc2452a85f200682a155ce89
X-Timestamp
1652081058.21552
Connection
keep-alive
Expires
Sun, 29 Mar 2026 03:01:49 GMT
Accept-Ranges
bytes
X-Trans-Id
tx51a987c2642b41939b72f-0067a4829edfw1
Content-Length
44153
Date
Thu, 15 May 2025 10:03:09 GMT
Last-Modified
Mon, 09 May 2022 07:24:19 GMT
Content-Type
image/png
GET
H/1.1
200
OK
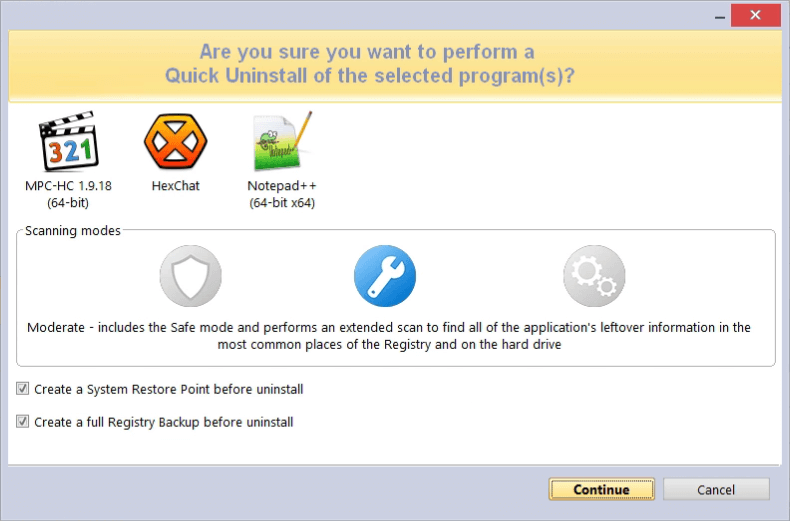
quick-multiple-uninstall.png
f057a20f961f56a72089-b74530d2d26278124f446233f95622ef.ssl.cf1.rackcdn.com/site/screens-5/
44 KB
45 KB
88ms
88ms
Image
image/png
23.57.20.115
AKAMAI-AS
General
Full URL
https://f057a20f961f56a72089-b74530d2d26278124f446233f95622ef.ssl.cf1.rackcdn.com/site/screens-5/quick-multiple-uninstall.png
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_256_GCM
Server
23.57.20.115 Düsseldorf, Germany, ASN16625 (AKAMAI-AS, US),
Reverse DNS
a23-57-20-115.deploy.static.akamaitechnologies.com
Software
/
Resource Hash
6bb1455c84f2e77d8fef44e02368071910a667b8edb24367c3f3ca9c4d2eca42

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

Origin
https://mycloud.rackspace.com
Cache-Control
public, max-age=39297
ETag
d8c7804b94ff102892e567488b3c5607
X-Timestamp
1652081058.20472
Connection
keep-alive
Expires
Thu, 15 May 2025 20:58:06 GMT
Accept-Ranges
bytes
X-Trans-Id
tx7ccf709d6ed44546bf50c-0066e43b26dfw1
Content-Length
45535
Date
Thu, 15 May 2025 10:03:09 GMT
Last-Modified
Mon, 09 May 2022 07:24:19 GMT
Content-Type
image/png
GET
H/1.1
200
OK
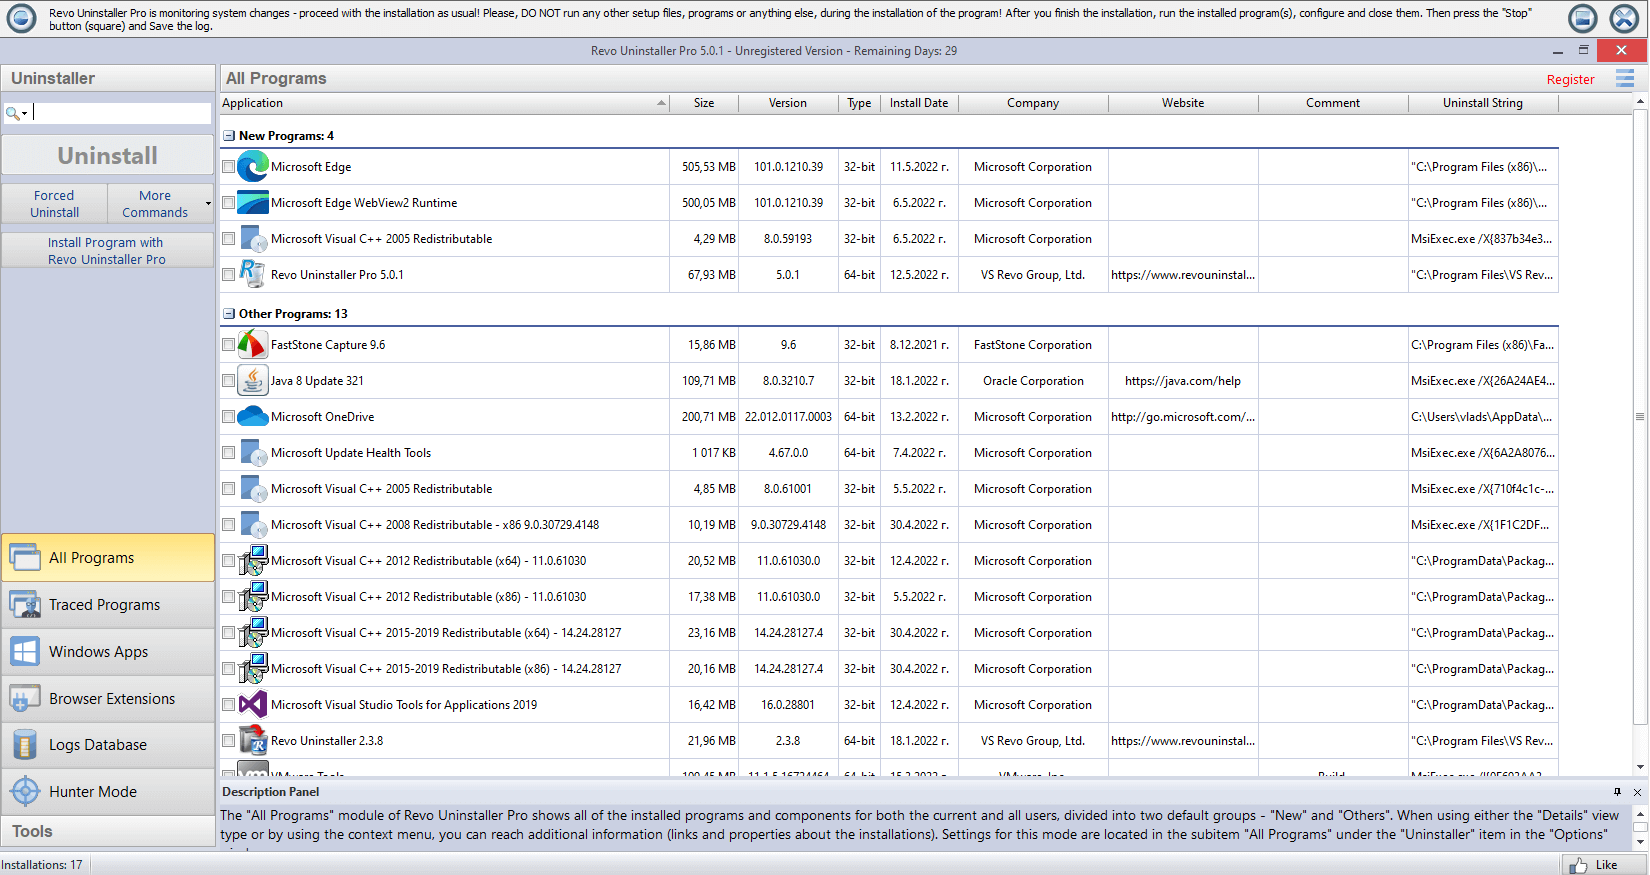
real-time-installation-monitor.png
f057a20f961f56a72089-b74530d2d26278124f446233f95622ef.ssl.cf1.rackcdn.com/site/screens-5/
69 KB
69 KB
83ms
83ms
Image
image/png
23.57.20.115
AKAMAI-AS
General
Full URL
https://f057a20f961f56a72089-b74530d2d26278124f446233f95622ef.ssl.cf1.rackcdn.com/site/screens-5/real-time-installation-monitor.png
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_256_GCM
Server
23.57.20.115 Düsseldorf, Germany, ASN16625 (AKAMAI-AS, US),
Reverse DNS
a23-57-20-115.deploy.static.akamaitechnologies.com
Software
/
Resource Hash
6625bc05fe0b30643675381684b69b0a7795863cac0cd88bc3967c9b23483ba2

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

Origin
https://mycloud.rackspace.com
Cache-Control
public, max-age=28553997
ETag
a5c572ce44fd3a42f00cc6bed12ed986
X-Timestamp
1652356197.05848
Connection
keep-alive
Expires
Fri, 10 Apr 2026 21:43:06 GMT
Accept-Ranges
bytes
X-Trans-Id
txe4b46d2d7c174d9994ce6-0067f83b6bdfw1
Content-Length
70602
Date
Thu, 15 May 2025 10:03:09 GMT
Last-Modified
Thu, 12 May 2022 11:49:58 GMT
Content-Type
image/png
GET
H/1.1
200
OK
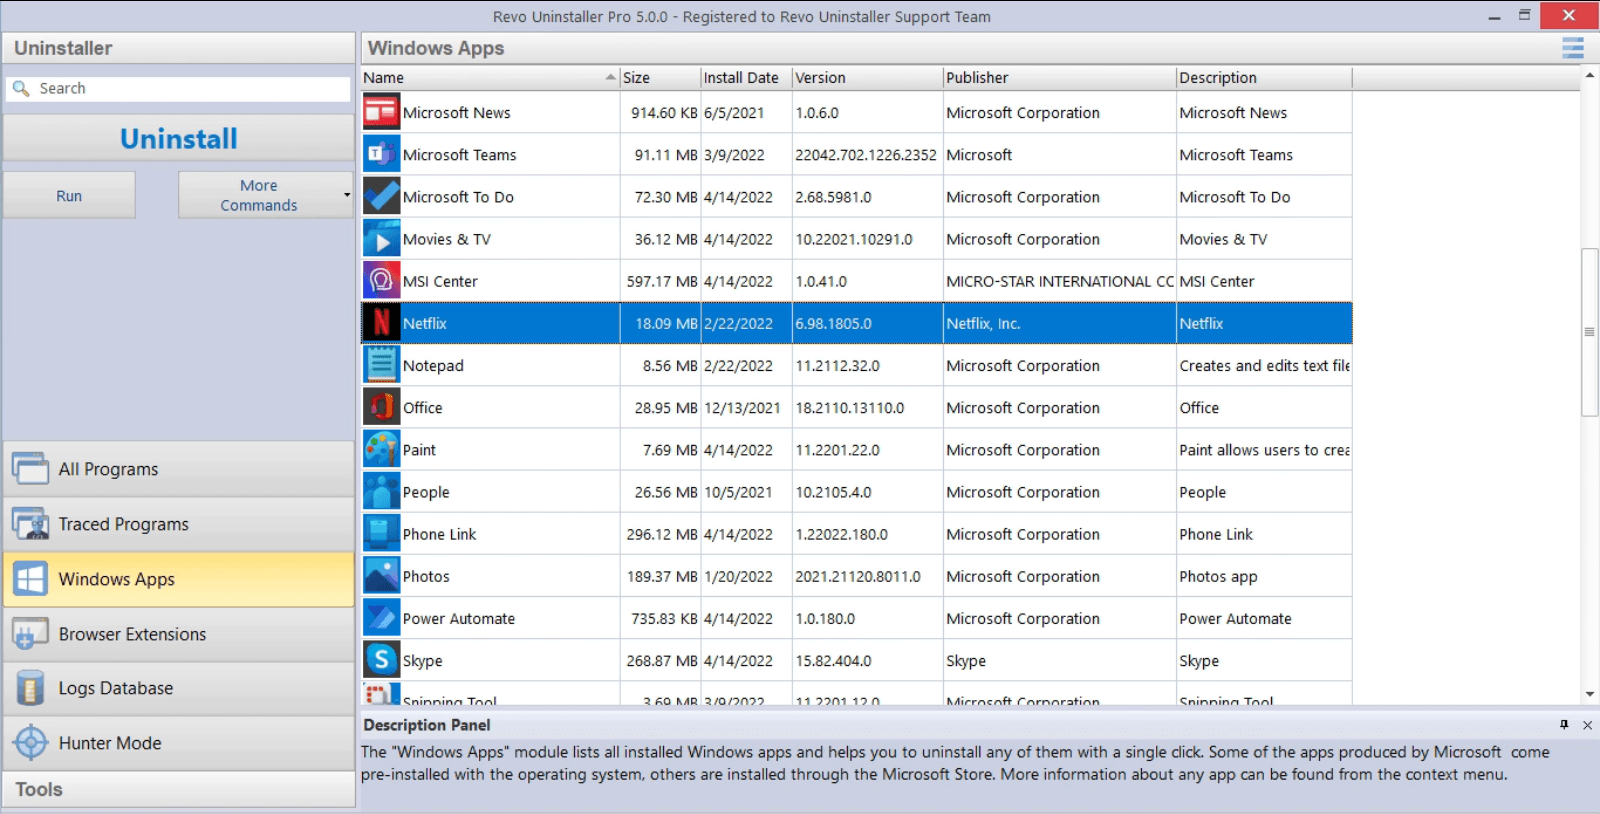
windows-apps.png
f057a20f961f56a72089-b74530d2d26278124f446233f95622ef.ssl.cf1.rackcdn.com/site/screens-5/
180 KB
180 KB
87ms
86ms
Image
image/png
23.57.20.115
AKAMAI-AS
General
Full URL
https://f057a20f961f56a72089-b74530d2d26278124f446233f95622ef.ssl.cf1.rackcdn.com/site/screens-5/windows-apps.png
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_256_GCM
Server
23.57.20.115 Düsseldorf, Germany, ASN16625 (AKAMAI-AS, US),
Reverse DNS
a23-57-20-115.deploy.static.akamaitechnologies.com
Software
/
Resource Hash
63cacefe7f2da164f756fd92658d8285f28e44e245c1632b4f675131e751bbd6

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

Origin
https://mycloud.rackspace.com
Cache-Control
public, max-age=31372619
ETag
3ac70e8793adde124fb90b65694ff1d9
X-Timestamp
1652081058.22500
Connection
keep-alive
Expires
Wed, 13 May 2026 12:40:08 GMT
Accept-Ranges
bytes
X-Trans-Id
tx046fddffc5794d2398aba-0068233da7dfw1
Content-Length
183810
Date
Thu, 15 May 2025 10:03:09 GMT
Last-Modified
Mon, 09 May 2022 07:24:19 GMT
Content-Type
image/png
GET
H2
200
pas-nc-embedded-v1.js Show response
app.mailjet.com/
14 KB
8 KB
208ms
88ms
Script
text/javascript
34.96.102.8
GOOGLE-CLOUD-PLAT...
General
Full URL
https://app.mailjet.com/pas-nc-embedded-v1.js
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.96.102.8 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM, US),
Reverse DNS
8.102.96.34.bc.googleusercontent.com
Software
/
Resource Hash
6040808e83425cfbe1205aafa193cbf31e09ceae50f32f1709ae2e1472bac545

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

cache-control
public, max-age=0
content-encoding
gzip
etag
W/"dc296a97a8352bb9de70ee545f0b2dac"
via
1.1 google
expires
Thu, 15 May 2025 10:03:09 GMT
accept-ranges
bytes
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 15 May 2025 10:03:09 GMT
content-type
text/javascript
last-modified
Wed, 14 May 2025 13:27:53 GMT
vary
Origin, Accept-Encoding
GET
H/1.1
200
OK
revo-uninstaller-logo-white.png
f057a20f961f56a72089-b74530d2d26278124f446233f95622ef.ssl.cf1.rackcdn.com/site/
2 KB
2 KB
81ms
79ms
Image
image/png
23.57.20.115
AKAMAI-AS
General
Full URL
https://f057a20f961f56a72089-b74530d2d26278124f446233f95622ef.ssl.cf1.rackcdn.com/site/revo-uninstaller-logo-white.png
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_256_GCM
Server
23.57.20.115 Düsseldorf, Germany, ASN16625 (AKAMAI-AS, US),
Reverse DNS
a23-57-20-115.deploy.static.akamaitechnologies.com
Software
/
Resource Hash
f3d0577d1af48acc04dc362dbd48e435471ada60e3a1c9a60e129c22e719fd17

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

Origin
https://mycloud.rackspace.com
Cache-Control
public, max-age=29592273
ETag
0c497999e8e20514eb1263f9823f3bb2
X-Timestamp
1592819788.33961
Connection
keep-alive
Expires
Wed, 22 Apr 2026 22:07:43 GMT
Accept-Ranges
bytes
X-Trans-Id
tx3782e2e42db64d24acb88-006808132edfw1
Content-Length
1975
Date
Thu, 15 May 2025 10:03:10 GMT
Last-Modified
Mon, 22 Jun 2020 09:56:29 GMT
Content-Type
image/png
GET
H2
200
snippet.js Show response
static.zdassets.com/ekr/
10 KB
5 KB
157ms
57ms
Script
application/javascript
216.198.54.3
CLOUDFLARESPECTRU...
General
Full URL
https://static.zdassets.com/ekr/snippet.js?key=4c200800-b795-45ba-8671-5fe06189f891
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
216.198.54.3 , United States, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
c7631939bbc2c74fc9a5fb1ee9565250a15bf95cc0e364da7fc5f15e3db41427
Security Headers
Name Value
Strict-Transport-Security max-age=0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

access-control-max-age
0
content-encoding
br
cf-cache-status
HIT
etag
W/"c88d625098ddb649cf216dba2e52435c"
x-amz-version-id
C4qpYKgeT8.DeRlre_wbz3El4DCj0uok
age
16
report-to
{"endpoints":[{"url":"https:\/\/a.nel.cloudflare.com\/report\/v4?s=fMeCPT845TC%2FhsOh5OBuvKY%2F8BdqYgHYBnxPRf3KnYm7594%2FvRvF8afE7VkX0ZwfcxHcC%2B6V0RZ7j2o6BPTzGkC7QGT1oBfcfN9W3lCbu%2BN47yR78KufXa7258Ajbdyq3%2FuA%2FFU%3D"}],"group":"cf-nel","max_age":604800}
access-control-allow-methods
GET, HEAD
date
Thu, 15 May 2025 10:03:09 GMT
content-type
application/javascript
last-modified
Mon, 04 Nov 2024 09:45:04 GMT
vary
Accept-Encoding
x-amz-id-2
bV2h0Cx99s67Nnhw4rURTew8r46ZkqFmSfBmAYOtPiXMfba8/NgxXlWW6GrrSkOeidoGvgntrQjK9bFnsXIhyDumfz7SGegutRmpXu6/nBk=
access-control-allow-headers
*
strict-transport-security
max-age=0
x-amz-replication-status
COMPLETED
cache-control
public, max-age=3600, s-maxage=60
nel
{"success_fraction":0,"report_to":"cf-nel","max_age":604800}
x-amz-request-id
F8AXJTF15HXGRPK2
cf-ray
9401cdcb0ecb94ef-LIS
access-control-allow-origin
*
server
cloudflare
x-amz-server-side-encryption
AES256
GET
H2
200
lazysizes.min.js Show response
www.revouninstaller.com/wp-content/plugins/autoptimize/classes/external/js/
10 KB
4 KB
146ms
144ms
Script
application/javascript
146.20.152.114
RACKSPACE
General
Full URL
https://www.revouninstaller.com/wp-content/plugins/autoptimize/classes/external/js/lazysizes.min.js?ao_version=3.1.13
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
146.20.152.114 , United States, ASN27357 (RACKSPACE, US),
Reverse DNS
1333686-web1.vsrevogroup.com
Software
XYZ /
Resource Hash
c4fada4accfa24704b54248bc5ce84acac50b6a059828b7714fe3006786c80c1
Security Headers
Name Value
Content-Security-Policy frame-ancestors 'self';
Strict-Transport-Security max-age=31536000; includeSubdomains
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 1; mode=block

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/free-install-thankyou/

Response headers

content-encoding
gzip
x-permitted-cross-domain-policies
none
x-content-type-options
nosniff
expires
max-age=A10368000, public
date
Thu, 15 May 2025 10:03:10 GMT
last-modified
Wed, 08 Jan 2025 06:09:47 GMT
vary
Accept-Encoding
content-type
application/javascript
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=31536000; includeSubdomains
content-security-policy
frame-ancestors 'self';
cache-control
max-age=0, private, no-store, no-cache, must-revalidate
referrer-policy
no-referrer, strict-origin-when-cross-origin
permissions-policy
interest-cohort=()
accept-ranges
bytes
content-length
4122
x-xss-protection
1; mode=block
server
XYZ
GET
H2
200
jquery.min.js Show response
ajax.googleapis.com/ajax/libs/jquery/3.5.1/
87 KB
31 KB
241ms
74ms
Script
text/javascript
142.250.185.234
GOOGLE
General
Full URL
https://ajax.googleapis.com/ajax/libs/jquery/3.5.1/jquery.min.js?ver=3.5.1
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.250.185.234 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
fra16s53-in-f10.1e100.net
Software
sffe /
Resource Hash
f7f6a5894f1d19ddad6fa392b2ece2c5e578cbf7da4ea805b6885eb6985b6e3d
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

content-encoding
gzip
age
140701
report-to
{"group":"hosted-libraries-pushers","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/hosted-libraries-pushers"}]}
x-content-type-options
nosniff
expires
Wed, 13 May 2026 18:58:09 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Tue, 13 May 2025 18:58:09 GMT
last-modified
Fri, 08 May 2020 07:05:03 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
cache-control
public, max-age=31536000, stale-while-revalidate=2592000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="hosted-libraries-pushers"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/hosted-libraries-pushers
accept-ranges
bytes
access-control-allow-origin
*
content-length
31021
x-xss-protection
0
server
sffe
GET
H2
200
popper.min.js Show response
cdn.jsdelivr.net/npm/popper.js@1.16.0/dist/umd/
21 KB
8 KB
159ms
53ms
Script
application/javascript
104.16.174.226
CLOUDFLARENET
General
Full URL
https://cdn.jsdelivr.net/npm/popper.js@1.16.0/dist/umd/popper.min.js?ver=1.16.0
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.16.174.226 -, , ASN13335 (CLOUDFLARENET, US),
Reverse DNS
Software
cloudflare /
Resource Hash
c776195ad46333c6c9a9fe3c74502ffea9a02faf122388ea3567922cc65a3060
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

access-control-expose-headers
*
content-encoding
br
cf-cache-status
HIT
etag
W/"5309-YvI45zNIx3656GVCan0bfeI8uy0"
age
1580211
report-to
{"endpoints":[{"url":"https:\/\/a.nel.cloudflare.com\/report\/v4?s=YDLxXalUvLgWJX9vxNAGSfH9TfUMSh9xkGX5UxRCvxmret5%2BGG65IAweffXq9tZ2dgjqblo3FXBTTzTO1amlEva5T4AisIQdf7eeUrCw7mWmAMRz7%2FdfJEjMUxeyXS97bnI%3D"}],"group":"cf-nel","max_age":604800}
x-content-type-options
nosniff
x-jsd-version-type
version
alt-svc
h3=":443"; ma=86400
x-cache
HIT, HIT
date
Thu, 15 May 2025 10:03:10 GMT
content-type
application/javascript; charset=utf-8
x-served-by
cache-fra-eddf8230104-FRA, cache-lga21956-LGA
vary
Accept-Encoding
strict-transport-security
max-age=31536000; includeSubDomains; preload
cache-control
public, max-age=31536000, s-maxage=31536000, immutable
timing-allow-origin
*
nel
{"success_fraction":0.01,"report_to":"cf-nel","max_age":604800}
cross-origin-resource-policy
cross-origin
cf-ray
9401cdcc1813e3d1-LIS
accept-ranges
bytes
access-control-allow-origin
*
content-length
7202
server
cloudflare
x-jsd-version
1.16.0
GET
H3
200
bootstrap.min.js Show response
stackpath.bootstrapcdn.com/bootstrap/4.4.1/js/
59 KB
17 KB
54ms
52ms
Script
application/javascript
104.18.10.207
CLOUDFLARENET
General
Full URL
https://stackpath.bootstrapcdn.com/bootstrap/4.4.1/js/bootstrap.min.js?ver=4.4.1
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.18.10.207 -, , ASN13335 (CLOUDFLARENET, US),
Reverse DNS
Software
cloudflare /
Resource Hash
5aa53525abc5c5200c70b3f6588388f86076cd699284c23cda64e92c372a1548
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

cdn-status
200
content-encoding
br
cf-cache-status
HIT
etag
"61f338f870fcd0ff46362ef109d28533"
age
2878658
x-content-type-options
nosniff
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Thu, 15 May 2025 10:03:10 GMT
last-modified
Mon, 25 Jan 2021 22:04:09 GMT
content-type
application/javascript; charset=utf-8
vary
Accept-Encoding
cdn-cache
HIT
cdn-cachedat
11/18/2024 16:55:16
cdn-requestpullcode
200
priority
u=2,i=?0
strict-transport-security
max-age=31536000; includeSubDomains; preload
cache-control
public, max-age=31919000
cdn-requestpullsuccess
True
timing-allow-origin
*
cdn-requesttime
0
cdn-uid
b1941f61-b576-4f40-80de-5677acb38f74
cdn-requestid
4ee2f1d52e8bd1caab713654cfb2e3c4
cross-origin-resource-policy
cross-origin
cdn-pullzone
252412
cdn-proxyver
1.07
cf-ray
9401cdcc08966932-LIS
access-control-allow-origin
*
cdn-edgestorageid
1221
server
cloudflare
cdn-requestcountrycode
FR
GET
H2
200
autoptimize_073e910834683dd15a87d718deaecd41.js Show response
www.revouninstaller.com/wp-content/cache/autoptimize/js/
19 KB
7 KB
153ms
151ms
Script
application/javascript
146.20.152.114
RACKSPACE
General
Full URL
https://www.revouninstaller.com/wp-content/cache/autoptimize/js/autoptimize_073e910834683dd15a87d718deaecd41.js
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
146.20.152.114 , United States, ASN27357 (RACKSPACE, US),
Reverse DNS
1333686-web1.vsrevogroup.com
Software
XYZ /
Resource Hash
941ce302a58a370422466e73e52f341477e5e10dbe976bb7dc4ef91821c28545
Security Headers
Name Value
Content-Security-Policy frame-ancestors 'self';
Strict-Transport-Security max-age=31536000; includeSubdomains
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 1; mode=block

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/free-install-thankyou/

Response headers

content-encoding
gzip
x-permitted-cross-domain-policies
none
x-content-type-options
nosniff
expires
max-age=A10368000, public
date
Thu, 15 May 2025 10:03:10 GMT
last-modified
Mon, 24 Feb 2025 13:05:05 GMT
vary
Accept-Encoding
content-type
application/javascript
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=31536000; includeSubdomains
content-security-policy
frame-ancestors 'self';
cache-control
max-age=0, private, no-store, no-cache, must-revalidate
referrer-policy
no-referrer, strict-origin-when-cross-origin
permissions-policy
interest-cohort=()
accept-ranges
bytes
content-length
6966
x-xss-protection
1; mode=block
server
XYZ
GET
H2
200
gtm.js Show response
www.googletagmanager.com/
436 KB
139 KB
314ms
114ms
Script
application/javascript
142.250.186.72
GOOGLE
General
Full URL
https://www.googletagmanager.com/gtm.js?id=GTM-T6G2J7
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.250.186.72 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
fra24s05-in-f8.1e100.net
Software
Google Tag Manager /
Resource Hash
2d1a1605140685d005db91fac1250f9d4b60566b565ab08740aa1c67ba4b104c
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

content-encoding
br
report-to
{"group":"ascgcycc:1317:0","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/scaffolding/ascgcycc:1317:0"}],}
expires
Thu, 15 May 2025 10:03:10 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 15 May 2025 10:03:10 GMT
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
last-modified
Thu, 15 May 2025 09:00:00 GMT
access-control-allow-headers
Cache-Control
strict-transport-security
max-age=31536000; includeSubDomains
cache-control
private, max-age=900
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
content-security-policy-report-only
script-src 'none'; form-action 'none'; frame-src 'none'; report-uri https://csp.withgoogle.com/csp/scaffolding/ascgcycc:1317:0
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to=ascgcycc:1317:0
content-length
141350
x-xss-protection
0
server
Google Tag Manager
GET
H2
200
css
fonts.googleapis.com/
29 KB
2 KB
287ms
87ms
Stylesheet
text/css
142.250.184.202
GOOGLE
General
Full URL
https://fonts.googleapis.com/css?family=Open+Sans:300,400,600,700,800&display=swap
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.250.184.202 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
fra24s11-in-f10.1e100.net
Software
ESF /
Resource Hash
688d6577ebeea79fd6e9ab9d09f9ac69a2cca4e6f2060776e9326aba482176bd
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

content-encoding
gzip
x-content-type-options
nosniff
expires
Thu, 15 May 2025 10:03:10 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 15 May 2025 10:03:10 GMT
content-type
text/css; charset=utf-8
vary
Sec-Fetch-Dest, Sec-Fetch-Mode, Sec-Fetch-Site
last-modified
Thu, 15 May 2025 09:07:11 GMT
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=31536000
link
<https://fonts.gstatic.com>; rel=preconnect; crossorigin
cache-control
private, max-age=86400, stale-while-revalidate=604800
timing-allow-origin
*
cross-origin-opener-policy
same-origin-allow-popups
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
x-xss-protection
0
server
ESF
GET
H2
200
banner.no-autoblock.js Show response
consent.cookiefirst.com/
103 KB
38 KB
94ms
93ms
Script
application/javascript
169.150.247.36
CDN77 Datacamp Li...
General
Full URL
https://consent.cookiefirst.com/banner.no-autoblock.js
Requested by
Host: consent.cookiefirst.com
URL: https://consent.cookiefirst.com/sites/revouninstaller.com-eaf2c1f3-7cb1-4b17-9342-3053be0001d7/consent.js?ver=025bcaeb072a0ece6e6e557f241bd7bd
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
169.150.247.36 Frankfurt am Main, Germany, ASN60068 (CDN77 Datacamp Limited, GB),
Reverse DNS
169-150-247-36.bunnyinfra.net
Software
Cookie First CDN-DE1-1079 /
Resource Hash
d2614cd932db07243a69aee3ec8797c765f5210d4b38795b77cc60fd74d7c2cf

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

cdn-status
200
access-control-expose-headers
Server, x-goog-meta-frames, Content-Length, Content-Type, Range, X-Requested-With, If-Modified-Since, If-None-Match, visitor-location
content-encoding
zstd
etag
"6821e19d-19d72"
cdn-fileserver
588
date
Thu, 15 May 2025 10:03:10 GMT
cdn-storageserver
DE-1019
last-modified
Mon, 12 May 2025 11:55:09 GMT
content-type
application/javascript
vary
Accept-Encoding
cdn-cache
HIT
access-control-allow-headers
Request-Id, Server, x-goog-meta-frames, Content-Length, Content-Type, Range, X-Requested-With, If-Modified-Since, If-None-Match, traceparent
cdn-requestpullcode
200
cdn-cachedat
05/12/2025 11:55:14
cache-control
public, max-age=1800
cdn-requestpullsuccess
True
visitor-location
PT
cdn-requesttime
0
cdn-uid
d602dab6-3f92-4809-a378-608fd2b89403
cdn-requestid
1937e9f4f75730a301798a46db774d51
cdn-pullzone
236985
cdn-proxyver
1.27
access-control-allow-origin
*
cdn-edgestorageid
1079
server
Cookie First CDN-DE1-1079
cdn-requestcountrycode
PT
GET
DATA
200
OK
truncated
/
67 B
0
Image
image/svg+xml

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
5c37189fb9387be170c36a9b799e1a6ce3f7f016a79b2c7032ed14be8597509c

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/svg+xml
GET
DATA
200
OK
truncated
/
350 B
0
Image
image/png

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
7bdc4fd1b52f88617553782da88299fc8551f6921d5a30c5a29b96cb8b4c3eae

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/png
GET
DATA
200
OK
truncated
/
357 B
0
Image
image/png

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
6434052af0ddf6b0203fc314c95448d2148edc35dab8973128a46430fd6152c2

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/png
GET
DATA
200
OK
truncated
/
271 B
0
Image
image/png

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
b7d183dce188ef91df5ddcd9ff5378e1b64ce515ccb048ed2a1f32d4fd0a0a3e

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/png
GET
DATA
200
OK
truncated
/
234 B
0
Image
image/png

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
5486d67c53956813c2ab1fdef773516ee85aff7adae4ae0186cf09e398c1e28f

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/png
GET
DATA
200
OK
truncated
/
360 B
0
Image
image/png

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
d5bbdcb19982fe95732f1402bd8cadcf407746cec57fa18043f6dd7b3dbf2502

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/png
GET
DATA
200
OK
truncated
/
353 B
0
Image
image/png

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
7dfe84faf51f33af5a66f356a57efcc53951f01c7529deb3e6edab005e72ae0d

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/png
GET
DATA
200
OK
truncated
/
265 B
0
Image
image/png

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
9bf6bf3dcc07223416fc8bbb8f49bff57d21c1c6dffd76f38f8c11e7d054c340

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/png
GET
DATA
200
OK
truncated
/
194 B
0
Image
image/png

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
0b8e6a0503148db0c445d26d7aef6a8de1d31b68a30f212ab47b6d4e7400f6bb

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/png
GET
DATA
200
OK
truncated
/
290 B
0
Image
image/png

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
ee43de7f6648dac36980de3bcf1bf0d34f07178fdb8afac80541f5cf1660cc5d

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/png
GET
DATA
200
OK
truncated
/
243 B
0
Image
image/png

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
c0da39dfab2a366de1c0efa54c349ef46cdb40d083882d3fc7530de710845cf2

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/png
GET
DATA
200
OK
truncated
/
239 B
0
Image
image/png

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
e956a757317f4346a99bc7317d6accf3ffb49c89a3e6a031eb2218de4af224f8

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/png
GET
DATA
200
OK
truncated
/
248 B
0
Image
image/png

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
3ad72d04b863fc860a2f724f27820ad7b2699614a91dcd4c0bdd06f57685ec75

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/png
GET
DATA
200
OK
truncated
/
294 B
0
Image
image/png

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
70643c4dd06e40c19d5f6ed2d0a5d448394cd21ab9b1d9650060dede45535a8a

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/png
GET
DATA
200
OK
truncated
/
214 B
0
Image
image/png

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
7a4e9eaad077165880b982842cc79f705c883e584c3fedaa1f2a97c016e697a3

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/png
GET
DATA
200
OK
truncated
/
252 B
0
Image
image/png

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
c9db31d43b24c3f411603160fc6554ceb91e1c628696646a13a563feddee0540

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/png
GET
DATA
200
OK
truncated
/
339 B
0
Image
image/png

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
296f5722ef36477feb23f79b20a628df8baf4527d29e16ff161a5bc95dca3890

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/png
GET
DATA
200
OK
truncated
/
68 B
0
Image
image/svg+xml

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
e69e78bce7fcba24d0b97671983c4ac0148d1cd9fb10e149d30be8b947c4eab4

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/svg+xml
GET
DATA
200
OK
truncated
/
68 B
0
Image
image/svg+xml

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
a7ae4f4e313e150000175511c29ca19ae2948eb663987253d19a9372cc20e3fe

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/svg+xml
GET
H/1.1
200
OK
uninstaller.png
f057a20f961f56a72089-b74530d2d26278124f446233f95622ef.ssl.cf1.rackcdn.com/site/screens-5/
115 KB
0
1ms
0ms
Image
image/png
23.57.20.115
AKAMAI-AS
General
Full URL
https://f057a20f961f56a72089-b74530d2d26278124f446233f95622ef.ssl.cf1.rackcdn.com/site/screens-5/uninstaller.png
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_256_GCM
Server
23.57.20.115 Düsseldorf, Germany, ASN16625 (AKAMAI-AS, US),
Reverse DNS
a23-57-20-115.deploy.static.akamaitechnologies.com
Software
/
Resource Hash
568849a9b53202c322377a9061b5f918fd01fffe5e76783afe5d323a1d6400a6

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

Origin
https://mycloud.rackspace.com
Cache-Control
public, max-age=27386169
ETag
c906d9048e7fd55333ed12d888b634e2
X-Timestamp
1652081058.19629
Expires
Sat, 28 Mar 2026 09:19:18 GMT
Accept-Ranges
bytes
X-Trans-Id
txff094752bb2646138bb99-00651d72d1dfw1
Content-Length
117465
Date
Thu, 15 May 2025 10:03:09 GMT
Last-Modified
Mon, 09 May 2022 07:24:19 GMT
Content-Type
image/png
GET
H/1.1
200
OK
forced-uninstall.png
f057a20f961f56a72089-b74530d2d26278124f446233f95622ef.ssl.cf1.rackcdn.com/site/screens-5/
43 KB
0
1ms
1ms
Image
image/png
23.57.20.115
AKAMAI-AS
General
Full URL
https://f057a20f961f56a72089-b74530d2d26278124f446233f95622ef.ssl.cf1.rackcdn.com/site/screens-5/forced-uninstall.png
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_256_GCM
Server
23.57.20.115 Düsseldorf, Germany, ASN16625 (AKAMAI-AS, US),
Reverse DNS
a23-57-20-115.deploy.static.akamaitechnologies.com
Software
/
Resource Hash
4302eac6f74fb5f3ff2229402ddb0bef9a518f8188319428d157159768fa2366

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

Origin
https://mycloud.rackspace.com
Cache-Control
public, max-age=27449920
ETag
7f4bffffbc2452a85f200682a155ce89
X-Timestamp
1652081058.21552
Expires
Sun, 29 Mar 2026 03:01:49 GMT
Accept-Ranges
bytes
X-Trans-Id
tx51a987c2642b41939b72f-0067a4829edfw1
Content-Length
44153
Date
Thu, 15 May 2025 10:03:09 GMT
Last-Modified
Mon, 09 May 2022 07:24:19 GMT
Content-Type
image/png
GET
DATA
200
OK
truncated
/
66 B
0
Image
image/svg+xml

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
639d02df457ed5e83465da0306131f5a083f17395434c2f474b2adc413692bd9

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/svg+xml
GET
DATA
200
OK
truncated
/
68 B
0
Image
image/svg+xml

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
b31c1f88534ee7c8830364c8c448069f88df370243dc6c55ca2f6cc97a1a717b

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/svg+xml
GET
H2
200
4c200800-b795-45ba-8671-5fe06189f891 Show response
ekr.zdassets.com/compose/
940 B
1 KB
723ms
573ms
Fetch
application/json
216.198.54.3
CLOUDFLARESPECTRU...
General
Full URL
https://ekr.zdassets.com/compose/4c200800-b795-45ba-8671-5fe06189f891
Requested by
Host: static.zdassets.com
URL: https://static.zdassets.com/ekr/snippet.js?key=4c200800-b795-45ba-8671-5fe06189f891
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
216.198.54.3 , United States, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
0c3217fe5cc4c6f1a2ea526e5e34167790df7661199b94e317ee720c8cec27ca
Security Headers
Name Value
Strict-Transport-Security max-age=0
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 1; mode=block

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

access-control-max-age
7200
x-request-id
938905ebb96d484e-SEA, 938905ebb96d484e-SEA, 938905ebb96d484e-SEA
access-control-expose-headers
content-encoding
br
cf-cache-status
HIT
etag
W/"0c3217fe5cc4c6f1a2ea526e5e341677"
x-permitted-cross-domain-policies
none
report-to
{"endpoints":[{"url":"https:\/\/a.nel.cloudflare.com\/report\/v4?s=UEGsBlurPtXlWY0RaLHcq%2Bvd7%2FP2Sb1AkfSu1mt8kP3NJ3PTjrAk0ACy5wLyFIokGlFpqt4CS3iraDld3kY%2BRXy7%2Blnr8YPfS8rLbExhvcXBh3k2ODvv5dSLKsOqqkAadu4%3D"}],"group":"cf-nel","max_age":604800}
access-control-allow-methods
GET, POST, OPTIONS
x-content-type-options
nosniff
date
Thu, 15 May 2025 10:03:10 GMT
content-type
application/json; charset=utf-8
vary
Accept, Origin, Accept-Encoding
x-runtime
0.020845
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=0
cdn-cache-control
max-age=60
cache-control
max-age=300, public, stale-while-revalidate=300, stale-if-error=21600
nel
{"success_fraction":0,"report_to":"cf-nel","max_age":604800}
referrer-policy
strict-origin-when-cross-origin
x-download-options
noopen
cf-ray
9401cdcd4e4648a4-LIS
access-control-allow-origin
*
x-zendesk-zorg
yes, yes
x-xss-protection
1; mode=block
server
cloudflare
GET
H2
200
version.json Show response
consent.cookiefirst.com/sites/revouninstaller.com-eaf2c1f3-7cb1-4b17-9342-3053be0001d7/
44 B
830 B
253ms
100ms
Fetch
application/json
169.150.247.36
CDN77 Datacamp Li...
General
Full URL
https://consent.cookiefirst.com/sites/revouninstaller.com-eaf2c1f3-7cb1-4b17-9342-3053be0001d7/version.json?v=1747303390218
Requested by
Host: consent.cookiefirst.com
URL: https://consent.cookiefirst.com/banner.no-autoblock.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
169.150.247.36 Frankfurt am Main, Germany, ASN60068 (CDN77 Datacamp Limited, GB),
Reverse DNS
169-150-247-36.bunnyinfra.net
Software
Cookie First CDN-DE1-1079 /
Resource Hash
24d7b59ef3e2a233984a1ae5558b9ea09e58e616ce5c0c707f126781869aeaec

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Accept
application/json
Referer
https://www.revouninstaller.com/

Response headers

cdn-status
200
access-control-expose-headers
Server, x-goog-meta-frames, Content-Length, Content-Type, Range, X-Requested-With, If-Modified-Since, If-None-Match, visitor-location
content-encoding
zstd
etag
"6815cfc9-2c"
cdn-fileserver
750
date
Thu, 15 May 2025 10:03:10 GMT
cdn-storageserver
DE-599
last-modified
Sat, 03 May 2025 08:11:53 GMT
content-type
application/json
vary
Accept-Encoding
cdn-cache
MISS
access-control-allow-headers
Request-Id, Server, x-goog-meta-frames, Content-Length, Content-Type, Range, X-Requested-With, If-Modified-Since, If-None-Match, traceparent
cdn-requestpullcode
200
cdn-cachedat
05/15/2025 10:03:10
cache-control
public, max-age=15
cdn-requestpullsuccess
True
visitor-location
PT
cdn-requesttime
0
cdn-uid
d602dab6-3f92-4809-a378-608fd2b89403
cdn-requestid
adb41c790075e146e980420c5def5da8
cdn-pullzone
236985
cdn-proxyver
1.27
access-control-allow-origin
*
cdn-edgestorageid
1079
server
Cookie First CDN-DE1-1079
cdn-requestcountrycode
PT
GET
DATA
200
OK
truncated
/
44 B
0
Image
image/webp

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
bd25bde9fc4427cd6f3babcb8f888fe6174ca48881c103e243d4c6f83f30aab6

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/webp
GET
DATA
200
OK
truncated
/
38 B
0
Image
image/webp

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
52dc24c0429ea6ccc5b579a6da8bb79bf41e471fe5108a62009f3c2e195551c0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/webp
GET
H/1.1
200
OK
revo-uninstaller-logo.png
f057a20f961f56a72089-b74530d2d26278124f446233f95622ef.ssl.cf1.rackcdn.com/site/
2 KB
2 KB
81ms
80ms
Image
image/png
23.57.20.115
AKAMAI-AS
General
Full URL
https://f057a20f961f56a72089-b74530d2d26278124f446233f95622ef.ssl.cf1.rackcdn.com/site/revo-uninstaller-logo.png
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_256_GCM
Server
23.57.20.115 Düsseldorf, Germany, ASN16625 (AKAMAI-AS, US),
Reverse DNS
a23-57-20-115.deploy.static.akamaitechnologies.com
Software
/
Resource Hash
4a43f37a56077705cd95fb9d3b20c5a660b3a2ffbab855f8730dcecb8432e496

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

Origin
https://mycloud.rackspace.com
Cache-Control
public, max-age=27509917
ETag
56792ce856fd50036d6df977e97aa0e4
X-Timestamp
1584727125.03954
Connection
keep-alive
Expires
Sun, 29 Mar 2026 19:41:47 GMT
Accept-Ranges
bytes
X-Trans-Id
txa924dd5d261f4323b0558-0065c9ac57dfw1
Content-Length
1847
Date
Thu, 15 May 2025 10:03:10 GMT
Last-Modified
Fri, 20 Mar 2020 17:58:46 GMT
Content-Type
image/png
GET
H/1.1
200
OK
100-guarantee.png
f057a20f961f56a72089-b74530d2d26278124f446233f95622ef.ssl.cf1.rackcdn.com/site/
4 KB
5 KB
80ms
80ms
Image
image/png
23.57.20.115
AKAMAI-AS
General
Full URL
https://f057a20f961f56a72089-b74530d2d26278124f446233f95622ef.ssl.cf1.rackcdn.com/site/100-guarantee.png
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_256_GCM
Server
23.57.20.115 Düsseldorf, Germany, ASN16625 (AKAMAI-AS, US),
Reverse DNS
a23-57-20-115.deploy.static.akamaitechnologies.com
Software
/
Resource Hash
898736a5f0d5891ededfcd9942475967c407a8f1243b28a6d3536ba98c44fbcb

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

Origin
https://mycloud.rackspace.com
Cache-Control
public, max-age=28790085
ETag
a5d0487eccbae5e8cc43a4129d4991d4
X-Timestamp
1727779531.42471
Connection
keep-alive
Expires
Mon, 13 Apr 2026 15:17:55 GMT
Accept-Ranges
bytes
X-Trans-Id
tx067870df396c4640a9ddf-006798fa5edfw1
Content-Length
4271
Date
Thu, 15 May 2025 10:03:10 GMT
Last-Modified
Tue, 01 Oct 2024 10:45:32 GMT
Content-Type
image/png
GET
H/1.1
200
OK
bundle-rup-rrg.webp
f057a20f961f56a72089-b74530d2d26278124f446233f95622ef.ssl.cf1.rackcdn.com/site/assets/
9 KB
10 KB
164ms
81ms
Image
image/webp
23.57.20.115
AKAMAI-AS
General
Full URL
https://f057a20f961f56a72089-b74530d2d26278124f446233f95622ef.ssl.cf1.rackcdn.com/site/assets/bundle-rup-rrg.webp
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_256_GCM
Server
23.57.20.115 Düsseldorf, Germany, ASN16625 (AKAMAI-AS, US),
Reverse DNS
a23-57-20-115.deploy.static.akamaitechnologies.com
Software
/
Resource Hash
330ee0ac92dec8a04ba432b9bf5d171330454e553cb46c18d96fdb925ee310dd

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

Origin
https://mycloud.rackspace.com
Cache-Control
public, max-age=27560566
ETag
5f289d5acf07662e37afb036ac8a299e
X-Timestamp
1741691122.29828
Connection
keep-alive
Expires
Mon, 30 Mar 2026 09:45:56 GMT
Accept-Ranges
bytes
X-Trans-Id
tx98c9c5b5093b47efa705d-0067e912dadfw1
Content-Length
9480
Date
Thu, 15 May 2025 10:03:10 GMT
Last-Modified
Tue, 11 Mar 2025 11:05:23 GMT
Content-Type
image/webp
GET
DATA
200
OK
truncated
/
82 B
0
Image
image/webp

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
7ce23bb169d56e3dc218181172c5d318dc16526e035b539e038f605a893ea551

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/webp
GET
DATA
200
OK
truncated
/
90 B
0
Image
image/webp

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
345a7f619e726c9ed21fa1e83646623f3491056eb1c9e0f3af797c42d38255c1

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/webp
GET
H/1.1
200
OK
revo-bg.webp
f057a20f961f56a72089-b74530d2d26278124f446233f95622ef.ssl.cf1.rackcdn.com/site/popup/
5 KB
5 KB
160ms
85ms
Image
image/webp
23.57.20.115
AKAMAI-AS
General
Full URL
https://f057a20f961f56a72089-b74530d2d26278124f446233f95622ef.ssl.cf1.rackcdn.com/site/popup/revo-bg.webp
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/wp-content/cache/autoptimize/css/autoptimize_single_43c6b5a3c1ca4c32d1940a3f2aaba505.css?ver=1.1
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_256_GCM
Server
23.57.20.115 Düsseldorf, Germany, ASN16625 (AKAMAI-AS, US),
Reverse DNS
a23-57-20-115.deploy.static.akamaitechnologies.com
Software
/
Resource Hash
501eff36e8442488336a3dd4d7532886979a6f2f062c4f094b519a78d508733f

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

Origin
https://mycloud.rackspace.com
Cache-Control
public, max-age=27324746
ETag
683db6035528caa9eebe8c020f07e74f
X-Timestamp
1741691440.58136
Connection
keep-alive
Expires
Fri, 27 Mar 2026 16:15:36 GMT
Accept-Ranges
bytes
X-Trans-Id
tx6e6b646e0ce64783b5cd7-0067d01a5bdfw1
Content-Length
4946
Date
Thu, 15 May 2025 10:03:10 GMT
Last-Modified
Tue, 11 Mar 2025 11:10:41 GMT
Content-Type
image/webp
GET
H2
200
css
fonts.googleapis.com/
29 KB
0
0ms
0ms
Stylesheet
text/css
142.250.184.202
GOOGLE
General
Full URL
https://fonts.googleapis.com/css?family=Open+Sans:300,400,600,700,800&display=swap
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.250.184.202 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
fra24s11-in-f10.1e100.net
Software
ESF /
Resource Hash
688d6577ebeea79fd6e9ab9d09f9ac69a2cca4e6f2060776e9326aba482176bd
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

content-encoding
gzip
x-content-type-options
nosniff
expires
Thu, 15 May 2025 10:03:10 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 15 May 2025 10:03:10 GMT
content-type
text/css; charset=utf-8
vary
Sec-Fetch-Dest, Sec-Fetch-Mode, Sec-Fetch-Site
last-modified
Thu, 15 May 2025 09:07:11 GMT
x-frame-options
SAMEORIGIN
link
<https://fonts.gstatic.com>; rel=preconnect; crossorigin
cache-control
private, max-age=86400, stale-while-revalidate=604800
timing-allow-origin
*
cross-origin-opener-policy
same-origin-allow-popups
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
x-xss-protection
0
server
ESF
GET
H2
200
index.html Show response
widget.trustpilot.com/trustboxes/5419b6a8b0d04a076446a9ad/ Frame EBB5
7 KB
2 KB
242ms
81ms
Document
text/html
52.222.236.107
AMAZON-02
General
Full URL
https://widget.trustpilot.com/trustboxes/5419b6a8b0d04a076446a9ad/index.html?templateId=5419b6a8b0d04a076446a9ad&businessunitId=600037798b18380001bcf594
Requested by
Host: widget.trustpilot.com
URL: https://widget.trustpilot.com/bootstrap/v5/tp.widget.bootstrap.min.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
52.222.236.107 , United States, ASN16509 (AMAZON-02, US),
Reverse DNS
server-52-222-236-107.fra56.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
402179b88fa6e0b17851d64725ec39658d804bd6cc9b8ba227e27bd3b4cca459
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

Referer
https://www.revouninstaller.com/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36

Response headers

age
81873
cache-control
max-age=86400
content-encoding
br
content-type
text/html
date
Wed, 14 May 2025 11:18:38 GMT
etag
W/"fc82fd18b089da00a381dd91b8df8463"
last-modified
Mon, 10 Feb 2025 13:11:35 GMT
server
AmazonS3
strict-transport-security
max-age=31536000
vary
accept-encoding
via
1.1 934706f40ffde6f857deae8d024c1192.cloudfront.net (CloudFront)
x-amz-cf-id
fgEZVWsuuZ-se4tUbDDOovUJBMTzvAG-QYQvHJ2zG4PfWxW8lMi5yg==
x-amz-cf-pop
FRA56-P4
x-amz-server-side-encryption
AES256
x-amz-version-id
null
x-cache
Hit from cloudfront
x-content-type-options
nosniff
x-xss-protection
1; mode=block
GET
H3
200
memvYaGs126MiZpBA-UvWbX2vVnXBbObj2OVTS-muw.woff2
fonts.gstatic.com/s/opensans/v40/
47 KB
47 KB
170ms
80ms
Font
font/woff2
216.58.206.35
GOOGLE
General
Full URL
https://fonts.gstatic.com/s/opensans/v40/memvYaGs126MiZpBA-UvWbX2vVnXBbObj2OVTS-muw.woff2
Requested by
Host: fonts.googleapis.com
URL: https://fonts.googleapis.com/css?family=Open+Sans:300,400,600,700,800&display=swap
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
216.58.206.35 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
lcfraa-aa-in-f3.1e100.net
Software
sffe /
Resource Hash
3c4d6a1421c7ddb7e404521fe8c4cd5be5af446d7689cd880be26612eaad3cfa
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Origin
https://www.revouninstaller.com
Referer
https://fonts.googleapis.com/

Response headers

age
182862
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Wed, 13 May 2026 07:15:28 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Tue, 13 May 2025 07:15:28 GMT
last-modified
Thu, 14 Dec 2023 02:08:40 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
48236
x-xss-protection
0
server
sffe
GET
H3
200
memvYaGs126MiZpBA-UvWbX2vVnXBbObj2OVTUGmu1aB.woff2
fonts.gstatic.com/s/opensans/v40/
24 KB
24 KB
170ms
82ms
Font
font/woff2
216.58.206.35
GOOGLE
General
Full URL
https://fonts.gstatic.com/s/opensans/v40/memvYaGs126MiZpBA-UvWbX2vVnXBbObj2OVTUGmu1aB.woff2
Requested by
Host: fonts.googleapis.com
URL: https://fonts.googleapis.com/css?family=Open+Sans:300,400,600,700,800&display=swap
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
216.58.206.35 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
lcfraa-aa-in-f3.1e100.net
Software
sffe /
Resource Hash
7e510e61c497d334da21eccda06df5d3a428c9ea94d6903b6138e7c7255aba0f
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Origin
https://www.revouninstaller.com
Referer
https://fonts.googleapis.com/

Response headers

age
139944
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Wed, 13 May 2026 19:10:46 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Tue, 13 May 2025 19:10:46 GMT
last-modified
Thu, 14 Dec 2023 02:04:54 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
24984
x-xss-protection
0
server
sffe
GET
H2
200
/ Show response
core.service.elfsight.com/p/boot/
9 KB
5 KB
320ms
214ms
XHR
application/json
104.22.69.95
CLOUDFLARENET
General
Full URL
https://core.service.elfsight.com/p/boot/?page=https%3A%2F%2Fwww.revouninstaller.com%2Ffree-install-thankyou%2F&w=6dc981f7-4958-43fa-99af-6578df9f304a
Requested by
Host: static.elfsight.com
URL: https://static.elfsight.com/platform/platform.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.22.69.95 -, , ASN13335 (CLOUDFLARENET, US),
Reverse DNS
Software
cloudflare /
Resource Hash
598f66a650667901cdce56b575211d5ab0fd5e0e164df032df0c63e9a12ebe42
Security Headers
Name Value
Strict-Transport-Security max-age=0
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0, 1; mode=block

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

content-encoding
gzip
cf-cache-status
DYNAMIC
etag
W/"24f5-EKIGjj1kDzAQJBVBsL5uliC7Qqk"
x-permitted-cross-domain-policies
none
x-content-type-options
nosniff
alt-svc
h3=":443"; ma=86400
date
Thu, 15 May 2025 10:03:10 GMT
content-type
application/json; charset=utf-8
vary
Accept-Encoding, Origin
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=0
x-dns-prefetch-control
on
cross-origin-opener-policy
unsafe-none
speculation-rules
"/cdn-cgi/speculation"
cross-origin-resource-policy
same-origin
access-control-allow-credentials
true
referrer-policy
no-referrer
x-download-options
noopen
cf-ray
9401cdcecaa911e6-LIS
access-control-allow-origin
https://www.revouninstaller.com
x-xss-protection
0, 1; mode=block
origin-agent-cluster
?1
server
cloudflare
cf-apo-via
origin,host
GET
H2
200
location Show response
edge.cookiefirst.com/prod/
66 B
492 B
255ms
89ms
Fetch
application/json
169.150.247.38
CDN77 Datacamp Li...
General
Full URL
https://edge.cookiefirst.com/prod/location?origin=www.revouninstaller.com
Requested by
Host: consent.cookiefirst.com
URL: https://consent.cookiefirst.com/banner.no-autoblock.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
169.150.247.38 Frankfurt am Main, Germany, ASN60068 (CDN77 Datacamp Limited, GB),
Reverse DNS
169-150-247-38.bunnyinfra.net
Software
BunnyCDN-DE1-1081 /
Resource Hash
89f154c58e6daffa0085f4d6ac74cbcdecbdd190fda50d34777265102458fb68

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Accept
application/json
Referer
https://www.revouninstaller.com/

Response headers

cdn-status
200
date
Thu, 15 May 2025 10:03:10 GMT
cdn-cache
BYPASS
content-type
application/json; charset=utf-8
cdn-cachedat
05/15/2025 10:03:10
cdn-requestpullcode
200
cache-control
public, max-age=1200
cdn-requestpullsuccess
True
cdn-requesttime
1
cdn-uid
d602dab6-3f92-4809-a378-608fd2b89403
cdn-requestid
5cb2f4a6b15e97dc0cef75bdcd296271
cdn-pullzone
717911
cdn-proxyver
1.27
access-control-allow-origin
https://www.revouninstaller.com
content-length
66
cdn-edgestorageid
1081
server
BunnyCDN-DE1-1081
cdn-requestcountrycode
PT
POST
H3
200
collect
www.google.com/ccm/
0
0
169ms
84ms
Fetch
text/plain
142.250.186.100
GOOGLE
General
Full URL
https://www.google.com/ccm/collect?en=page_view&dl=https%3A%2F%2Fwww.revouninstaller.com%2Ffree-install-thankyou%2F&scrsrc=www.googletagmanager.com&frm=0&rnd=1179787254.1747303391&dt=Thank%20you%20for%20installing%20Revo%20Uninstaller%20Free&auid=315310286.1747303391&navt=n&npa=1&gtm=45He55d1v71855269za200&gcd=13l3l3l2l1l1&dma_cps=syphamo&dma=1&tag_exp=101509157~103116026~103130498~103130500~103200004~103233427~103252644~103252646~103301114~103301116&tft=1747303390549&tfd=2113&apve=1&apvf=f
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtm.js?id=GTM-T6G2J7
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.250.186.100 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
fra24s06-in-f4.1e100.net
Software
/
Resource Hash

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

GET
H2
200
js Show response
www.googletagmanager.com/gtag/
445 KB
145 KB
128ms
127ms
Script
application/javascript
142.250.186.72
GOOGLE
General
Full URL
https://www.googletagmanager.com/gtag/js?id=G-P73P80145H&cx=c&gtm=45He55d1v71855269za200&tag_exp=101509157~103116026~103130498~103130500~103200004~103233427~103252644~103252646~103301114~103301116
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtm.js?id=GTM-T6G2J7
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.250.186.72 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
fra24s05-in-f8.1e100.net
Software
Google Tag Manager /
Resource Hash
3daa33db1794c557a0c63358f0ac20ffc31890f841c406df16d5894c1319a07e
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

content-encoding
br
report-to
{"group":"ascgcycc:1075:0","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/scaffolding/ascgcycc:1075:0"}],}
expires
Thu, 15 May 2025 10:03:10 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 15 May 2025 10:03:10 GMT
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
access-control-allow-headers
Cache-Control
strict-transport-security
max-age=31536000; includeSubDomains
cache-control
private, max-age=900
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
content-security-policy-report-only
script-src 'none'; form-action 'none'; frame-src 'none'; report-uri https://csp.withgoogle.com/csp/scaffolding/ascgcycc:1075:0
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to=ascgcycc:1075:0
content-length
147911
x-xss-protection
0
server
Google Tag Manager
GET
H2
200
analytics.js Show response
www.google-analytics.com/
52 KB
21 KB
247ms
62ms
Script
text/javascript
216.239.38.178
GOOGLE
General
Full URL
https://www.google-analytics.com/analytics.js
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtm.js?id=GTM-T6G2J7
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
216.239.38.178 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
Software
Golfe2 /
Resource Hash
de36e50194320a7d3ef1ace9bd34a875a8bd458b253c061979dd628e9bf49afd
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

content-encoding
gzip
age
3250
report-to
{"group":"ascnsrsgac:225:0","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/scaffolding/ascnsrsgac:225:0"}],}
x-content-type-options
nosniff
expires
Thu, 15 May 2025 11:09:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 15 May 2025 09:09:00 GMT
last-modified
Tue, 12 Dec 2023 18:09:08 GMT
content-type
text/javascript
vary
Accept-Encoding
strict-transport-security
max-age=31536000; includeSubDomains; preload
cache-control
public, max-age=7200
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
script-src 'none'; form-action 'none'; frame-src 'none'; report-uri https://csp.withgoogle.com/csp/scaffolding/ascnsrsgac:225:0
cross-origin-opener-policy-report-only
same-origin; report-to=ascnsrsgac:225:0
content-length
20994
server
Golfe2
GET
H3
200
fbevents.js Show response
connect.facebook.net/en_US/
272 KB
69 KB
163ms
81ms
Script
application/x-javascript
157.240.252.13
FACEBOOK
General
Full URL
https://connect.facebook.net/en_US/fbevents.js
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
157.240.252.13 Frankfurt am Main, Germany, ASN32934 (FACEBOOK, US),
Reverse DNS
xx-fbcdn-shv-01-fra3.fbcdn.net
Software
/
Resource Hash
d077807b2373375b2d5c8ffbfeeea0bcb152e29c21ec147aecfab6b5502e5463
Security Headers
Name Value
Content-Security-Policy default-src 'self' blob: facebook.net *.facebook.net facebook.com *.facebook.com fbcdn.net *.fbcdn.net fbsbx.com *.fbsbx.com cdninstagram.com *.cdninstagram.com;script-src data: 'nonce-R4Y7nEwr' *.facebook.com *.fbcdn.net *.facebook.net 127.0.0.1:* blob: 'self';style-src 'self' data: blob: 'unsafe-inline';connect-src 'self' data: blob: *.facebook.com facebook.com *.fbcdn.net *.facebook.net wss://*.facebook.com:* wss://*.fbcdn.net attachment.fbsbx.com ws://localhost:* *.cdninstagram.com;font-src 'self' data: blob: facebook.net *.facebook.net facebook.com *.facebook.com fbcdn.net *.fbcdn.net fbsbx.com *.fbsbx.com cdninstagram.com *.cdninstagram.com;img-src 'self' data: blob: facebook.net *.facebook.net facebook.com *.facebook.com fbcdn.net *.fbcdn.net fbsbx.com *.fbsbx.com cdninstagram.com *.cdninstagram.com;media-src 'self' data: blob: facebook.net *.facebook.net facebook.com *.facebook.com fbcdn.net *.fbcdn.net fbsbx.com *.fbsbx.com cdninstagram.com *.cdninstagram.com;child-src 'self' data: blob: facebook.net *.facebook.net facebook.com *.facebook.com fbcdn.net *.fbcdn.net fbsbx.com *.fbsbx.com cdninstagram.com *.cdninstagram.com;frame-src 'self' data: blob: facebook.net *.facebook.net facebook.com *.facebook.com fbcdn.net *.fbcdn.net fbsbx.com *.fbsbx.com cdninstagram.com *.cdninstagram.com;manifest-src 'self' data: blob: facebook.net *.facebook.net facebook.com *.facebook.com fbcdn.net *.fbcdn.net fbsbx.com *.fbsbx.com cdninstagram.com *.cdninstagram.com;object-src 'self' data: blob: facebook.net *.facebook.net facebook.com *.facebook.com fbcdn.net *.fbcdn.net fbsbx.com *.fbsbx.com cdninstagram.com *.cdninstagram.com;worker-src 'self' data: blob: facebook.net *.facebook.net facebook.com *.facebook.com fbcdn.net *.fbcdn.net fbsbx.com *.fbsbx.com cdninstagram.com *.cdninstagram.com;block-all-mixed-content;upgrade-insecure-requests;report-uri https://www.facebook.com/csp/reporting/?m=c&minimize=0;require-trusted-types-for 'script';
Strict-Transport-Security max-age=31536000; preload; includeSubDomains
X-Content-Type-Options nosniff
X-Frame-Options DENY
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

content-encoding
gzip
report-to
{"max_age":2592000,"endpoints":[{"url":"https:\/\/www.facebook.com\/browser_reporting\/coop\/?minimize=0"}],"group":"coop_report","include_subdomains":true}, {"max_age":86400,"endpoints":[{"url":"https:\/\/www.facebook.com\/browser_reporting\/coep\/?minimize=0"}],"group":"coep_report"}, {"max_age":21600,"endpoints":[{"url":"https:\/\/www.facebook.com\/ajax\/browser_error_reports\/"}],"group":"permissions_policy"}
x-content-type-options
nosniff
expires
Sat, 01 Jan 2000 00:00:00 GMT
alt-svc
h3=":443"; ma=86400
date
Thu, 15 May 2025 10:03:10 GMT
content-type
application/x-javascript; charset=utf-8
vary
Accept-Encoding
cross-origin-embedder-policy-report-only
require-corp;report-to="coep_report"
priority
u=3,i
x-frame-options
DENY
strict-transport-security
max-age=31536000; preload; includeSubDomains
reporting-endpoints
coop_report="https://www.facebook.com/browser_reporting/coop/?minimize=0", coep_report="https://www.facebook.com/browser_reporting/coep/?minimize=0", permissions_policy="https://www.facebook.com/ajax/browser_error_reports/"
content-security-policy
default-src 'self' blob: facebook.net *.facebook.net facebook.com *.facebook.com fbcdn.net *.fbcdn.net fbsbx.com *.fbsbx.com cdninstagram.com *.cdninstagram.com;script-src data: 'nonce-R4Y7nEwr' *.facebook.com *.fbcdn.net *.facebook.net 127.0.0.1:* blob: 'self';style-src 'self' data: blob: 'unsafe-inline';connect-src 'self' data: blob: *.facebook.com facebook.com *.fbcdn.net *.facebook.net wss://*.facebook.com:* wss://*.fbcdn.net attachment.fbsbx.com ws://localhost:* *.cdninstagram.com;font-src 'self' data: blob: facebook.net *.facebook.net facebook.com *.facebook.com fbcdn.net *.fbcdn.net fbsbx.com *.fbsbx.com cdninstagram.com *.cdninstagram.com;img-src 'self' data: blob: facebook.net *.facebook.net facebook.com *.facebook.com fbcdn.net *.fbcdn.net fbsbx.com *.fbsbx.com cdninstagram.com *.cdninstagram.com;media-src 'self' data: blob: facebook.net *.facebook.net facebook.com *.facebook.com fbcdn.net *.fbcdn.net fbsbx.com *.fbsbx.com cdninstagram.com *.cdninstagram.com;child-src 'self' data: blob: facebook.net *.facebook.net facebook.com *.facebook.com fbcdn.net *.fbcdn.net fbsbx.com *.fbsbx.com cdninstagram.com *.cdninstagram.com;frame-src 'self' data: blob: facebook.net *.facebook.net facebook.com *.facebook.com fbcdn.net *.fbcdn.net fbsbx.com *.fbsbx.com cdninstagram.com *.cdninstagram.com;manifest-src 'self' data: blob: facebook.net *.facebook.net facebook.com *.facebook.com fbcdn.net *.fbcdn.net fbsbx.com *.fbsbx.com cdninstagram.com *.cdninstagram.com;object-src 'self' data: blob: facebook.net *.facebook.net facebook.com *.facebook.com fbcdn.net *.fbcdn.net fbsbx.com *.fbsbx.com cdninstagram.com *.cdninstagram.com;worker-src 'self' data: blob: facebook.net *.facebook.net facebook.com *.facebook.com fbcdn.net *.fbcdn.net fbsbx.com *.fbsbx.com cdninstagram.com *.cdninstagram.com;block-all-mixed-content;upgrade-insecure-requests;report-uri https://www.facebook.com/csp/reporting/?m=c&minimize=0;require-trusted-types-for 'script';
cache-control
public, max-age=1200
timing-allow-origin
*
cross-origin-opener-policy
same-origin-allow-popups
x-fb-connection-quality
GOOD; q=0.7, rtt=77, rtx=0, c=23, mss=1232, tbw=4805, tp=9, tpl=0, uplat=1, ullat=-1
pragma
public
x-fb-debug
DXn4UHOKbSMXv5unWeEcnSJlgya2R23yBrlwCQ9Fv3jVPT0mjxXfayzUBmFZN3elOHb/SSFAzzPf2AHAsB9rHg==
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
default-src 'self' blob: facebook.net *.facebook.net facebook.com *.facebook.com fbcdn.net *.fbcdn.net fbsbx.com *.fbsbx.com cdninstagram.com *.cdninstagram.com;script-src 'nonce-R4Y7nEwr' 'report-sample' *.facebook.com *.fbcdn.net *.facebook.net 127.0.0.1:* blob: 'self' data:;style-src 'self' data: blob: 'unsafe-inline';connect-src 'self' data: blob: *.facebook.com facebook.com *.fbcdn.net *.facebook.net wss://*.facebook.com:* wss://*.fbcdn.net attachment.fbsbx.com ws://localhost:* *.cdninstagram.com;font-src 'self' data: blob: facebook.net *.facebook.net facebook.com *.facebook.com fbcdn.net *.fbcdn.net fbsbx.com *.fbsbx.com cdninstagram.com *.cdninstagram.com;img-src 'self' data: blob: facebook.net *.facebook.net facebook.com *.facebook.com fbcdn.net *.fbcdn.net fbsbx.com *.fbsbx.com cdninstagram.com *.cdninstagram.com;media-src 'self' data: blob: facebook.net *.facebook.net facebook.com *.facebook.com fbcdn.net *.fbcdn.net fbsbx.com *.fbsbx.com cdninstagram.com *.cdninstagram.com;child-src 'self' data: blob: facebook.net *.facebook.net facebook.com *.facebook.com fbcdn.net *.fbcdn.net fbsbx.com *.fbsbx.com cdninstagram.com *.cdninstagram.com;frame-src 'self' data: blob: facebook.net *.facebook.net facebook.com *.facebook.com fbcdn.net *.fbcdn.net fbsbx.com *.fbsbx.com cdninstagram.com *.cdninstagram.com;manifest-src 'self' data: blob: facebook.net *.facebook.net facebook.com *.facebook.com fbcdn.net *.fbcdn.net fbsbx.com *.fbsbx.com cdninstagram.com *.cdninstagram.com;object-src 'self' data: blob: facebook.net *.facebook.net facebook.com *.facebook.com fbcdn.net *.fbcdn.net fbsbx.com *.fbsbx.com cdninstagram.com *.cdninstagram.com;worker-src 'self' data: blob: facebook.net *.facebook.net facebook.com *.facebook.com fbcdn.net *.fbcdn.net fbsbx.com *.fbsbx.com cdninstagram.com *.cdninstagram.com;report-uri https://www.facebook.com/csp/reporting/?m=c&minimize=0;require-trusted-types-for 'script';
permissions-policy
accelerometer=(), attribution-reporting=(), autoplay=(), bluetooth=(), camera=(), ch-device-memory=(), ch-downlink=(), ch-dpr=(), ch-ect=(), ch-rtt=(), ch-save-data=(), ch-ua-arch=(), ch-ua-bitness=(), ch-viewport-height=(), ch-viewport-width=(), ch-width=(), clipboard-read=(), clipboard-write=(), compute-pressure=(), display-capture=(), encrypted-media=(), fullscreen=(self), gamepad=(), geolocation=(), gyroscope=(), hid=(), idle-detection=(), interest-cohort=(), keyboard-map=(), local-fonts=(), magnetometer=(), microphone=(), midi=(), otp-credentials=(), payment=(), picture-in-picture=(), private-state-token-issuance=(), publickey-credentials-get=(), screen-wake-lock=(), serial=(), shared-storage=(), shared-storage-select-url=(), private-state-token-redemption=(), usb=(), unload=(self), window-management=(), xr-spatial-tracking=();report-to="permissions_policy"
document-policy
force-load-at-top
content-length
70067
x-xss-protection
0
origin-agent-cluster
?1
GET
H2
200
uwt.js Show response
static.ads-twitter.com/
57 KB
16 KB
258ms
80ms
Script
application/javascript
146.75.116.157
FASTLY
General
Full URL
https://static.ads-twitter.com/uwt.js
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
146.75.116.157 Frankfurt am Main, Germany, ASN54113 (FASTLY, US),
Reverse DNS
Software
/
Resource Hash
96e803cc46ba31cef48752356a13dc8a92564f2e6b20adcd4d360410b5fbc579

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

vary
Accept-Encoding,Host
cache-control
no-cache
content-encoding
gzip
etag
"89be6341362180b7e00592aa62f11b75+gzip+gzip"
accept-ranges
bytes
x-cache
HIT, HIT
p3p
CP="CAO DSP LAW CURa ADMa DEVa TAIa PSAa PSDa IVAa IVDa OUR BUS IND UNI COM NAV INT"
content-length
15757
date
Thu, 15 May 2025 10:03:10 GMT
x-tw-cdn
FT
last-modified
Mon, 28 Apr 2025 14:35:26 GMT
content-type
application/javascript; charset=utf-8
x-served-by
cache-iad-kjyo7100064-IAD, cache-fra-eddf8230037-FRA
x-amz-server-side-encryption
AES256
GET
H2
200
sw_iframe.html Show response
www.googletagmanager.com/static/service_worker/5570/ Frame 6412
3 KB
2 KB
237ms
78ms
Document
text/html
142.250.186.72
GOOGLE
General
Full URL
https://www.googletagmanager.com/static/service_worker/5570/sw_iframe.html?origin=https%3A%2F%2Fwww.revouninstaller.com
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtm.js?id=GTM-T6G2J7
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.250.186.72 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
fra24s05-in-f8.1e100.net
Software
sffe /
Resource Hash
d36b373b44b77f016e4b7df913ba2da2a8025456f016bc794861f210c0e3ada3
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36

Response headers

accept-ranges
bytes
age
8776
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cache-control
public, max-age=31536000
content-encoding
br
content-length
1482
content-type
text/html
cross-origin-opener-policy
same-origin; report-to="analytics-container-tag-serving"
cross-origin-resource-policy
cross-origin
date
Thu, 15 May 2025 07:36:54 GMT
expires
Fri, 15 May 2026 07:36:54 GMT
last-modified
Wed, 07 May 2025 08:58:00 GMT
report-to
{"group":"analytics-container-tag-serving","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/analytics-container-tag-serving"}]}
server
sffe
service-worker-allowed
/static/service_worker
vary
Accept-Encoding
x-content-type-options
nosniff
x-xss-protection
0
GET
H2
200
main.js Show response
widget.trustpilot.com/trustboxes/5419b6a8b0d04a076446a9ad/ Frame EBB5
55 KB
16 KB
98ms
98ms
Script
application/javascript
52.222.236.107
AMAZON-02
General
Full URL
https://widget.trustpilot.com/trustboxes/5419b6a8b0d04a076446a9ad/main.js
Requested by
Host: widget.trustpilot.com
URL: https://widget.trustpilot.com/trustboxes/5419b6a8b0d04a076446a9ad/index.html?templateId=5419b6a8b0d04a076446a9ad&businessunitId=600037798b18380001bcf594
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
52.222.236.107 , United States, ASN16509 (AMAZON-02, US),
Reverse DNS
server-52-222-236-107.fra56.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
2f193d706417bcf72a130968908edcd09a192c51f4b592114ea4697ee4dfe85b
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://widget.trustpilot.com/trustboxes/5419b6a8b0d04a076446a9ad/index.html?templateId=5419b6a8b0d04a076446a9ad&businessunitId=600037798b18380001bcf594

Response headers

content-encoding
br
x-amz-version-id
null
etag
W/"0661e82e1e81e92cd72dd68fb8c66a6a"
age
81873
x-content-type-options
nosniff
x-cache
Hit from cloudfront
x-amz-cf-id
zE1lvUmMvPMvRDyp9q3yzV6Dskf7t1FvQHrjMSNlDcUFwP8aifTGBw==
date
Wed, 14 May 2025 11:18:38 GMT
content-type
application/javascript;charset=utf-8
vary
accept-encoding
last-modified
Mon, 10 Feb 2025 13:11:40 GMT
strict-transport-security
max-age=31536000
cache-control
max-age=86400
via
1.1 934706f40ffde6f857deae8d024c1192.cloudfront.net (CloudFront)
x-xss-protection
1; mode=block
x-amz-cf-pop
FRA56-P4
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H2
200
formBuilder.js Show response
static.elfsight.com/apps/form-builder/stable/274292b12c2c7489e79d9a0da37845f9c90336c2/app/
932 KB
280 KB
85ms
83ms
Script
application/javascript
104.22.69.95
CLOUDFLARENET
General
Full URL
https://static.elfsight.com/apps/form-builder/stable/274292b12c2c7489e79d9a0da37845f9c90336c2/app/formBuilder.js
Requested by
Host: static.elfsight.com
URL: https://static.elfsight.com/platform/platform.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.22.69.95 -, , ASN13335 (CLOUDFLARENET, US),
Reverse DNS
Software
cloudflare /
Resource Hash
38fd706cbe82da3c705e708d889851bc1565dafc9a3d72d4c5527e7bcf13a933
Security Headers
Name Value
Strict-Transport-Security max-age=0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

content-encoding
gzip
cf-cache-status
BYPASS
etag
W/"9e81ad76186d8b2c48ea830d6c6e1c62"
alt-svc
h3=":443"; ma=86400
date
Thu, 15 May 2025 10:03:10 GMT
x-rgw-object-type
Normal
content-type
application/javascript; charset=utf-8
last-modified
Wed, 14 May 2025 08:51:03 GMT
vary
Origin, Access-Control-Request-Headers, Access-Control-Request-Method, Accept-Encoding
x-do-cdn-uuid
e32c40dc-02c3-4408-a6ec-51bfedff6dd9
strict-transport-security
max-age=0
cache-control
max-age=3600
speculation-rules
"/cdn-cgi/speculation"
x-amz-request-id
tx00000317fd9b13b5b77e1-00682459ba-16262b4a-sfo2b
cf-ray
9401cdd029651df8-LIS
server
cloudflare
GET
H2
200
5419b6a8b0d04a076446a9ad Show response
widget.trustpilot.com/trustbox-data/ Frame EBB5
1 KB
983 B
88ms
85ms
XHR
application/json
52.222.236.107
AMAZON-02
General
Full URL
https://widget.trustpilot.com/trustbox-data/5419b6a8b0d04a076446a9ad?businessUnitId=600037798b18380001bcf594&locale=en-US
Requested by
Host: widget.trustpilot.com
URL: https://widget.trustpilot.com/trustboxes/5419b6a8b0d04a076446a9ad/main.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
52.222.236.107 , United States, ASN16509 (AMAZON-02, US),
Reverse DNS
server-52-222-236-107.fra56.r.cloudfront.net
Software
Kestrel /
Resource Hash
2ad82d5c83c9ec058a1efbb568c497093d249190abad9d51bcd42869683fddb1
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Content-type
application/x-www-form-urlencoded
Referer
https://widget.trustpilot.com/trustboxes/5419b6a8b0d04a076446a9ad/index.html?templateId=5419b6a8b0d04a076446a9ad&businessunitId=600037798b18380001bcf594

Response headers

strict-transport-security
max-age=31536000
cache-control
public,max-age=1800
content-encoding
gzip
etag
"94a9b636bda4b921cca9951388df87ad"
age
159
x-content-type-options
nosniff
via
1.1 934706f40ffde6f857deae8d024c1192.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
aMkDaohA87DUacdAbaWgM1L-PIhpi3G41gpRDfSHhIXvjvEsfo1TEw==
x-xss-protection
1; mode=block
date
Thu, 15 May 2025 10:01:36 GMT
content-type
application/json; charset=utf-8
vary
accept-encoding
server
Kestrel
x-amz-cf-pop
FRA56-P4
GET
H2
204
TrustboxImpression Show response
widget.trustpilot.com/stats/ Frame EBB5
0
309 B
117ms
114ms
XHR
text/plain
52.222.236.107
AMAZON-02
General
Full URL
https://widget.trustpilot.com/stats/TrustboxImpression?locale=en-US&styleHeight=24px&styleWidth=100%25&theme=light&styleAlignment=center&url=https%3A%2F%2Fwww.revouninstaller.com%2Ffree-install-thankyou%2F&referrer=&userAgent=Mozilla%2F5.0%20(X11%3B%20Linux%20x86_64)%20AppleWebKit%2F537.36%20(KHTML%2C%20like%20Gecko)%20Chrome%2F136.0.0.0%20Safari%2F537.36&language=pt-PT&platform=Linux%20x86_64&nosettings=1&businessUnitId=600037798b18380001bcf594&widgetId=5419b6a8b0d04a076446a9ad
Requested by
Host: widget.trustpilot.com
URL: https://widget.trustpilot.com/trustboxes/5419b6a8b0d04a076446a9ad/main.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
52.222.236.107 , United States, ASN16509 (AMAZON-02, US),
Reverse DNS
server-52-222-236-107.fra56.r.cloudfront.net
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Content-type
application/x-www-form-urlencoded
Referer
https://widget.trustpilot.com/trustboxes/5419b6a8b0d04a076446a9ad/index.html?templateId=5419b6a8b0d04a076446a9ad&businessunitId=600037798b18380001bcf594

Response headers

strict-transport-security
max-age=31536000
cache-control
no-store,no-cache
pragma
no-cache
x-content-type-options
nosniff
via
1.1 934706f40ffde6f857deae8d024c1192.cloudfront.net (CloudFront)
x-cache
Miss from cloudfront
x-amz-cf-id
s8KDk79TxmHdyzvDHlPW7H85Pgja6iJoe7AVnv2NhxSkOdgcGZs3QA==
date
Thu, 15 May 2025 10:03:10 GMT
x-xss-protection
1; mode=block
x-amz-cf-pop
FRA56-P4
GET
H2
204
TrustboxView Show response
widget.trustpilot.com/stats/ Frame EBB5
0
310 B
116ms
113ms
XHR
text/plain
52.222.236.107
AMAZON-02
General
Full URL
https://widget.trustpilot.com/stats/TrustboxView?locale=en-US&styleHeight=24px&styleWidth=100%25&theme=light&styleAlignment=center&url=https%3A%2F%2Fwww.revouninstaller.com%2Ffree-install-thankyou%2F&referrer=&userAgent=Mozilla%2F5.0%20(X11%3B%20Linux%20x86_64)%20AppleWebKit%2F537.36%20(KHTML%2C%20like%20Gecko)%20Chrome%2F136.0.0.0%20Safari%2F537.36&language=pt-PT&platform=Linux%20x86_64&nosettings=1&businessUnitId=600037798b18380001bcf594&widgetId=5419b6a8b0d04a076446a9ad
Requested by
Host: widget.trustpilot.com
URL: https://widget.trustpilot.com/trustboxes/5419b6a8b0d04a076446a9ad/main.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
52.222.236.107 , United States, ASN16509 (AMAZON-02, US),
Reverse DNS
server-52-222-236-107.fra56.r.cloudfront.net
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Content-type
application/x-www-form-urlencoded
Referer
https://widget.trustpilot.com/trustboxes/5419b6a8b0d04a076446a9ad/index.html?templateId=5419b6a8b0d04a076446a9ad&businessunitId=600037798b18380001bcf594

Response headers

strict-transport-security
max-age=31536000
cache-control
no-store,no-cache
pragma
no-cache
x-content-type-options
nosniff
via
1.1 934706f40ffde6f857deae8d024c1192.cloudfront.net (CloudFront)
x-cache
Miss from cloudfront
x-amz-cf-id
ZP2D65XXnkwNTxX_HABN19lmiXtwNtx2dy5IlKYkggARmkCaWzx0Bw==
date
Thu, 15 May 2025 10:03:10 GMT
x-xss-protection
1; mode=block
x-amz-cf-pop
FRA56-P4
GET
H2
200
lang-widget-en.json Show response
consent.cookiefirst.com/sites/revouninstaller.com-eaf2c1f3-7cb1-4b17-9342-3053be0001d7/
13 KB
6 KB
88ms
87ms
Fetch
application/json
169.150.247.36
CDN77 Datacamp Li...
General
Full URL
https://consent.cookiefirst.com/sites/revouninstaller.com-eaf2c1f3-7cb1-4b17-9342-3053be0001d7/lang-widget-en.json?v=7bd5a67b-168c-4f03-8306-4d32216ee01f
Requested by
Host: consent.cookiefirst.com
URL: https://consent.cookiefirst.com/banner.no-autoblock.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
169.150.247.36 Frankfurt am Main, Germany, ASN60068 (CDN77 Datacamp Limited, GB),
Reverse DNS
169-150-247-36.bunnyinfra.net
Software
Cookie First CDN-DE1-1079 /
Resource Hash
afabc7377364e0e73475342d61d6e519e833aa63806db5fc8043458c8fa711b5

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Accept
application/json
Referer
https://www.revouninstaller.com/

Response headers

cdn-status
200
access-control-expose-headers
Server, x-goog-meta-frames, Content-Length, Content-Type, Range, X-Requested-With, If-Modified-Since, If-None-Match, visitor-location
content-encoding
zstd
etag
"6815cfbf-3582"
cdn-fileserver
599
date
Thu, 15 May 2025 10:03:10 GMT
cdn-storageserver
DE-1024
last-modified
Sat, 03 May 2025 08:11:43 GMT
content-type
application/json
vary
Accept-Encoding
cdn-cache
HIT
access-control-allow-headers
Request-Id, Server, x-goog-meta-frames, Content-Length, Content-Type, Range, X-Requested-With, If-Modified-Since, If-None-Match, traceparent
cdn-requestpullcode
200
cdn-cachedat
05/08/2025 14:18:55
cache-control
public, max-age=31919000
cdn-requestpullsuccess
True
visitor-location
PT
cdn-requesttime
0
cdn-uid
d602dab6-3f92-4809-a378-608fd2b89403
cdn-requestid
25d50394c8de89d5c333324230ea2fa0
cdn-pullzone
236985
cdn-proxyver
1.27
access-control-allow-origin
*
cdn-edgestorageid
1079
server
Cookie First CDN-DE1-1079
cdn-requestcountrycode
PT
GET
H3
200
502397613272382 Show response
connect.facebook.net/signals/config/
76 KB
15 KB
288ms
287ms
Script
application/x-javascript
157.240.252.13
FACEBOOK
General
Full URL
https://connect.facebook.net/signals/config/502397613272382?v=2.9.201&r=stable&domain=www.revouninstaller.com&hme=9ebdfdd473ffce6bfe2267012c83f73483198ffe20d84139a2066b7682f827c0&ex_m=73%2C128%2C113%2C117%2C64%2C6%2C106%2C72%2C19%2C100%2C92%2C54%2C57%2C181%2C202%2C209%2C205%2C206%2C208%2C32%2C107%2C56%2C80%2C207%2C176%2C179%2C203%2C204%2C189%2C139%2C44%2C194%2C191%2C192%2C37%2C151%2C18%2C53%2C198%2C197%2C141%2C21%2C43%2C2%2C46%2C68%2C69%2C70%2C74%2C96%2C20%2C17%2C99%2C95%2C94%2C114%2C55%2C116%2C42%2C115%2C33%2C97%2C29%2C177%2C180%2C148%2C14%2C15%2C16%2C8%2C9%2C28%2C25%2C26%2C60%2C65%2C67%2C78%2C105%2C108%2C30%2C79%2C12%2C10%2C83%2C51%2C24%2C110%2C109%2C111%2C102%2C13%2C23%2C4%2C41%2C77%2C22%2C160%2C89%2C135%2C76%2C1%2C98%2C59%2C87%2C36%2C31%2C85%2C86%2C91%2C40%2C7%2C93%2C84%2C47%2C35%2C38%2C0%2C71%2C118%2C90%2C5%2C50%2C49%2C101%2C88%2C246%2C174%2C126%2C163%2C156%2C3%2C39%2C66%2C45%2C112%2C48%2C82%2C63%2C62%2C34%2C103%2C61%2C58%2C52%2C81%2C75%2C27%2C104%2C11%2C119
Requested by
Host: connect.facebook.net
URL: https://connect.facebook.net/en_US/fbevents.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
157.240.252.13 Frankfurt am Main, Germany, ASN32934 (FACEBOOK, US),
Reverse DNS
xx-fbcdn-shv-01-fra3.fbcdn.net
Software
/
Resource Hash
fa0ca55c4ef6b064ff606cebee35597e67c781e4186dd51344a6492c0d3ec672
Security Headers
Name Value
Content-Security-Policy default-src 'self' blob: *;script-src data: 'nonce-7twqbRx2' *.facebook.com *.fbcdn.net *.facebook.net 127.0.0.1:* blob: 'self' https://*.google-analytics.com *.google.com;style-src 'self' data: blob: 'unsafe-inline';connect-src 'self' data: blob: *.facebook.com facebook.com *.fbcdn.net *.facebook.net wss://*.facebook.com:* wss://*.whatsapp.com:* wss://*.fbcdn.net attachment.fbsbx.com ws://localhost:* *.cdninstagram.com https://*.google-analytics.com;font-src 'self' data: blob: *;img-src 'self' data: blob: * https://*.google-analytics.com;media-src 'self' data: blob: *;child-src 'self' data: blob: *;frame-src 'self' data: blob: *;manifest-src 'self' data: blob: *;object-src 'self' data: blob: *;worker-src 'self' data: blob: *;block-all-mixed-content;upgrade-insecure-requests;require-trusted-types-for 'script';
Strict-Transport-Security max-age=31536000; preload; includeSubDomains
X-Content-Type-Options nosniff
X-Frame-Options DENY
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

content-encoding
gzip
report-to
{"max_age":2592000,"endpoints":[{"url":"https:\/\/www.facebook.com\/browser_reporting\/coop\/?minimize=0"}],"group":"coop_report","include_subdomains":true}, {"max_age":86400,"endpoints":[{"url":"https:\/\/www.facebook.com\/browser_reporting\/coep\/?minimize=0"}],"group":"coep_report"}, {"max_age":21600,"endpoints":[{"url":"https:\/\/www.facebook.com\/ajax\/browser_error_reports\/"}],"group":"permissions_policy"}
x-content-type-options
nosniff
expires
Sat, 01 Jan 2000 00:00:00 GMT
alt-svc
h3=":443"; ma=86400
date
Thu, 15 May 2025 10:03:11 GMT
content-type
application/x-javascript; charset=utf-8
vary
Accept-Encoding
cross-origin-embedder-policy-report-only
require-corp;report-to="coep_report"
priority
u=3,i
x-frame-options
DENY
strict-transport-security
max-age=31536000; preload; includeSubDomains
reporting-endpoints
coop_report="https://www.facebook.com/browser_reporting/coop/?minimize=0", coep_report="https://www.facebook.com/browser_reporting/coep/?minimize=0", permissions_policy="https://www.facebook.com/ajax/browser_error_reports/"
content-security-policy
default-src 'self' blob: *;script-src data: 'nonce-7twqbRx2' *.facebook.com *.fbcdn.net *.facebook.net 127.0.0.1:* blob: 'self' https://*.google-analytics.com *.google.com;style-src 'self' data: blob: 'unsafe-inline';connect-src 'self' data: blob: *.facebook.com facebook.com *.fbcdn.net *.facebook.net wss://*.facebook.com:* wss://*.whatsapp.com:* wss://*.fbcdn.net attachment.fbsbx.com ws://localhost:* *.cdninstagram.com https://*.google-analytics.com;font-src 'self' data: blob: *;img-src 'self' data: blob: * https://*.google-analytics.com;media-src 'self' data: blob: *;child-src 'self' data: blob: *;frame-src 'self' data: blob: *;manifest-src 'self' data: blob: *;object-src 'self' data: blob: *;worker-src 'self' data: blob: *;block-all-mixed-content;upgrade-insecure-requests;require-trusted-types-for 'script';
cache-control
public, max-age=1200
timing-allow-origin
*
cross-origin-opener-policy
same-origin-allow-popups
x-fb-connection-quality
GOOD; q=0.7, rtt=78, rtx=0, c=85, mss=1232, tbw=81285, tp=75, tpl=0, uplat=207, ullat=0
pragma
public
x-fb-debug
pHAsQdClOAo5MURAnxwYIX2FLuRIe6tHFTW24EG5knzMJ3/bQkVLSkh/jxicew8Ja74jro2twSdjTdWZVkPWNw==
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
default-src 'self' blob: *;script-src 'nonce-7twqbRx2' 'report-sample' *.facebook.com *.fbcdn.net *.facebook.net 127.0.0.1:* blob: 'self' data: https://*.google-analytics.com *.google.com;style-src 'self' data: blob: 'unsafe-inline';connect-src 'self' data: blob: *.facebook.com facebook.com *.fbcdn.net *.facebook.net wss://*.facebook.com:* wss://*.whatsapp.com:* wss://*.fbcdn.net attachment.fbsbx.com ws://localhost:* *.cdninstagram.com https://*.google-analytics.com;font-src 'self' data: blob: *;img-src 'self' data: blob: * https://*.google-analytics.com;media-src 'self' data: blob: *;child-src 'self' data: blob: *;frame-src 'self' data: blob: *;manifest-src 'self' data: blob: *;object-src 'self' data: blob: *;worker-src 'self' data: blob: *;report-uri https://www.facebook.com/csp/reporting/?minimize=0;require-trusted-types-for 'script';
permissions-policy
accelerometer=(), attribution-reporting=(), autoplay=(), bluetooth=(), camera=(), ch-device-memory=(), ch-downlink=(), ch-dpr=(), ch-ect=(), ch-rtt=(), ch-save-data=(), ch-ua-arch=(), ch-ua-bitness=(), ch-viewport-height=(), ch-viewport-width=(), ch-width=(), clipboard-read=(), clipboard-write=(), compute-pressure=(), display-capture=(), encrypted-media=(), fullscreen=(self), gamepad=(), geolocation=(), gyroscope=(), hid=(), idle-detection=(), interest-cohort=(), keyboard-map=(), local-fonts=(), magnetometer=(), microphone=(), midi=(), otp-credentials=(), payment=(), picture-in-picture=(), private-state-token-issuance=(), publickey-credentials-get=(), screen-wake-lock=(), serial=(), shared-storage=(), shared-storage-select-url=(), private-state-token-redemption=(), usb=(), unload=(self), window-management=(), xr-spatial-tracking=();report-to="permissions_policy"
document-policy
force-load-at-top
x-xss-protection
0
origin-agent-cluster
?1
GET
H2
200
web-widget-main-4138c17.js Show response
static.zdassets.com/web_widget/classic/latest/ Frame 65CC
830 KB
258 KB
75ms
74ms
Script
application/javascript
216.198.54.3
CLOUDFLARESPECTRU...
General
Full URL
https://static.zdassets.com/web_widget/classic/latest/web-widget-main-4138c17.js
Requested by
Host: static.zdassets.com
URL: https://static.zdassets.com/ekr/snippet.js?key=4c200800-b795-45ba-8671-5fe06189f891
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
216.198.54.3 , United States, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
69294444ea55c3f1d0b1ef7524cbc7def9c8255f178518d511a195c94fd72c68
Security Headers
Name Value
Strict-Transport-Security max-age=0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

access-control-max-age
0
content-encoding
br
cf-cache-status
HIT
etag
W/"5001f6910e590158564fd24c3ceb42f6"
x-amz-version-id
U_oHyHqrbEf2iYg7sJ88UEFzopCNZy2Z
age
1266535
report-to
{"endpoints":[{"url":"https:\/\/a.nel.cloudflare.com\/report\/v4?s=QKEyMsZkjZPZ9%2B44i%2BKqGV%2BoaFNmvnskqHcbPYnubstVE7d5jY%2BccmsnW%2FmmoJUl4HVuZTidUeEKt4ynD83ZJzUnu%2BuDHQ73iAHqnyjdc%2BGcY7poGFkUC1ykFNtDj5BxNS%2BGCX4%3D"}],"group":"cf-nel","max_age":604800}
access-control-allow-methods
GET, HEAD
expires
Thu, 30 Apr 2026 14:47:35 GMT
date
Thu, 15 May 2025 10:03:10 GMT
content-type
application/javascript; charset=utf-8
last-modified
Wed, 30 Apr 2025 14:47:36 GMT
vary
Accept-Encoding
x-amz-id-2
AipSxjW7uPsTAuQ48QGMabop5lcHelU8MfViDAq+9hI2yp3UFVVlxIMEnEWOJc3j7ROI3vA6kOn7oU6PnHlSWg==
access-control-allow-headers
*
strict-transport-security
max-age=0
x-amz-replication-status
COMPLETED
cache-control
public, max-age=31536000
nel
{"success_fraction":0,"report_to":"cf-nel","max_age":604800}
x-amz-request-id
PRMAVP7VGC5YHSNT
cf-ray
9401cdd1292194ef-LIS
access-control-allow-origin
*
server
cloudflare
x-amz-server-side-encryption
AES256
GET
H2
200
adsct
t.co/i/
43 B
645 B
257ms
160ms
Image
image/gif
162.159.140.229
CLOUDFLARENET
General
Full URL
https://t.co/i/adsct?bci=3&dv=Atlantic%2FAzores%26en-US%2Cen%26Google%20Inc.%26Linux%20x86_64%26255%261600%261200%266%2624%261600%261200%260%26na&eci=2&event_id=69e521af-3b23-4f6d-aa69-6a235dff5096&events=%5B%5B%22pageview%22%2C%7B%7D%5D%5D&integration=advertiser&p_id=Twitter&p_user_id=0&pl_id=4f3e2bbe-268e-4f2d-8805-bdab20070889&tw_document_href=https%3A%2F%2Fwww.revouninstaller.com%2Ffree-install-thankyou%2F&tw_iframe_status=0&tw_order_quantity=0&tw_sale_amount=0&txn_id=o6f2q&type=javascript&version=2.3.33
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
162.159.140.229 -, , ASN13335 (CLOUDFLARENET, US),
Reverse DNS
Software
cloudflare tsa_b /
Resource Hash
ac8778041fdb7f2e08ceb574c9a766247ea26f1a7d90fa854c4efcf4b361a957
Security Headers
Name Value
Strict-Transport-Security max-age=0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

strict-transport-security
max-age=0
x-transaction-id
1cbb845853d144df
cache-control
no-cache, no-store, max-age=0
x-connection-hash
ca1c5683ed140734c8398ced39e1dcdbf600ee157ff1f28022d9dd4d56bab95d
cf-cache-status
DYNAMIC
cf-ray
9401cdd1eac5950c-LIS
x-response-time
5
content-length
43
date
Thu, 15 May 2025 10:03:11 GMT
content-type
image/gif;charset=utf-8
perf
7402827104
server
cloudflare tsa_b
GET
H2
200
adsct
analytics.twitter.com/i/
43 B
667 B
344ms
244ms
Image
image/gif
172.66.0.227
CLOUDFLARENET
General
Full URL
https://analytics.twitter.com/i/adsct?bci=3&dv=Atlantic%2FAzores%26en-US%2Cen%26Google%20Inc.%26Linux%20x86_64%26255%261600%261200%266%2624%261600%261200%260%26na&eci=2&event_id=69e521af-3b23-4f6d-aa69-6a235dff5096&events=%5B%5B%22pageview%22%2C%7B%7D%5D%5D&integration=advertiser&p_id=Twitter&p_user_id=0&pl_id=4f3e2bbe-268e-4f2d-8805-bdab20070889&tw_document_href=https%3A%2F%2Fwww.revouninstaller.com%2Ffree-install-thankyou%2F&tw_iframe_status=0&tw_order_quantity=0&tw_sale_amount=0&txn_id=o6f2q&type=javascript&version=2.3.33
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.66.0.227 , United States, ASN13335 (CLOUDFLARENET, US),
Reverse DNS
Software
cloudflare tsa_b /
Resource Hash
ac8778041fdb7f2e08ceb574c9a766247ea26f1a7d90fa854c4efcf4b361a957
Security Headers
Name Value
Strict-Transport-Security max-age=631138519

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

strict-transport-security
max-age=631138519
x-transaction-id
9b6130ccb9bb7ab7
cache-control
no-cache, no-store, max-age=0
x-connection-hash
734acc2df5cd1b46c9e548ebf101b174d64c96c67f432df4f279ee8ebefd6c26
cf-cache-status
DYNAMIC
cf-ray
9401cdd1eda2e3b1-LIS
x-response-time
85
content-length
43
date
Thu, 15 May 2025 10:03:11 GMT
content-type
image/gif;charset=utf-8
perf
7402827104
server
cloudflare tsa_b
POST
H2
200
collect Show response
www.google-analytics.com/j/
3 B
458 B
78ms
59ms
XHR
text/plain
216.239.38.178
GOOGLE
General
Full URL
https://www.google-analytics.com/j/collect?v=1&_v=j101&a=1600420042&t=pageview&_s=1&dl=https%3A%2F%2Fwww.revouninstaller.com%2Ffree-install-thankyou%2F&ul=pt-pt&de=UTF-8&dt=Thank%20you%20for%20installing%20Revo%20Uninstaller%20Free&sd=24-bit&sr=1600x1200&vp=1600x1200&je=0&_u=YGBACEABBAAAACAAI~&jid=1861936288&gjid=1468601292&cid=1371600675.1747303391&tid=UA-1917045-1&_gid=1809515989.1747303391&_r=1&_slc=1&gtm=45He55d1n71T6G2J7v71855269za200&gcd=13l3l3l2l1l1&dma_cps=syphamo&dma=1&tag_exp=101509157~103116026~103130498~103130500~103200004~103233427~103252644~103252646~103301114~103301116&npa=1&z=1550362359
Requested by
Host: www.google-analytics.com
URL: https://www.google-analytics.com/analytics.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
216.239.38.178 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
Software
Golfe2 /
Resource Hash
1cffc2b3146584685cd72751d7f28aa030ab9ae2f1bc78f2c27909f8d8287b26
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Content-Type
text/plain
Referer
https://www.revouninstaller.com/

Response headers

report-to
{"group":"ascnsrsgac:175:0","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/scaffolding/ascnsrsgac:175:0"}],}
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 15 May 2025 10:03:10 GMT
last-modified
Sun, 17 May 1998 03:00:00 GMT
content-type
text/plain
cache-control
no-cache, no-store, must-revalidate
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
content-security-policy-report-only
script-src 'none'; form-action 'none'; frame-src 'none'; report-uri https://csp.withgoogle.com/csp/scaffolding/ascnsrsgac:175:0
access-control-allow-origin
https://www.revouninstaller.com
cross-origin-opener-policy-report-only
same-origin; report-to=ascnsrsgac:175:0
content-length
3
server
Golfe2
GET
H2
200
207.3869.c.js Show response
consent.cookiefirst.com/banner/v2.15.9/static-main-no-autoblock/
7 KB
4 KB
86ms
84ms
Script
application/javascript
169.150.247.36
CDN77 Datacamp Li...
General
Full URL
https://consent.cookiefirst.com/banner/v2.15.9/static-main-no-autoblock/207.3869.c.js
Requested by
Host: consent.cookiefirst.com
URL: https://consent.cookiefirst.com/banner.no-autoblock.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
169.150.247.36 Frankfurt am Main, Germany, ASN60068 (CDN77 Datacamp Limited, GB),
Reverse DNS
169-150-247-36.bunnyinfra.net
Software
Cookie First CDN-DE1-1079 /
Resource Hash
d120ab6f69b81ca09bbd82efab8e2e472d15e2233a7d765d3c7a1c2e1945dc95

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

cdn-status
200
access-control-expose-headers
Server, x-goog-meta-frames, Content-Length, Content-Type, Range, X-Requested-With, If-Modified-Since, If-None-Match, visitor-location
content-encoding
zstd
etag
"6821e19d-1a1f"
cdn-fileserver
862
date
Thu, 15 May 2025 10:03:10 GMT
cdn-storageserver
DE-637
last-modified
Mon, 12 May 2025 11:55:09 GMT
content-type
application/javascript
vary
Accept-Encoding
cdn-cache
HIT
access-control-allow-headers
Request-Id, Server, x-goog-meta-frames, Content-Length, Content-Type, Range, X-Requested-With, If-Modified-Since, If-None-Match, traceparent
cdn-requestpullcode
200
cdn-cachedat
05/12/2025 11:55:10
cache-control
public, max-age=31919000
cdn-requestpullsuccess
True
visitor-location
PT
cdn-requesttime
0
cdn-uid
d602dab6-3f92-4809-a378-608fd2b89403
cdn-requestid
303484fbb4d4164b435ad4831a529496
cdn-pullzone
236985
cdn-proxyver
1.27
access-control-allow-origin
*
cdn-edgestorageid
1079
server
Cookie First CDN-DE1-1079
cdn-requestcountrycode
PT
GET
H2
200
441.5ee5.c.css
consent.cookiefirst.com/banner/v2.15.9/static-main-no-autoblock/
19 KB
6 KB
86ms
85ms
Stylesheet
text/css
169.150.247.36
CDN77 Datacamp Li...
General
Full URL
https://consent.cookiefirst.com/banner/v2.15.9/static-main-no-autoblock/441.5ee5.c.css
Requested by
Host: consent.cookiefirst.com
URL: https://consent.cookiefirst.com/banner.no-autoblock.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
169.150.247.36 Frankfurt am Main, Germany, ASN60068 (CDN77 Datacamp Limited, GB),
Reverse DNS
169-150-247-36.bunnyinfra.net
Software
Cookie First CDN-DE1-1079 /
Resource Hash
ae5652f3e21d76b7d544f5fb02ab35c38799b897fd789675f110dbf1966e90a7

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

cdn-status
200
access-control-expose-headers
Server, x-goog-meta-frames, Content-Length, Content-Type, Range, X-Requested-With, If-Modified-Since, If-None-Match, visitor-location
content-encoding
zstd
etag
"6821e19d-4dcf"
cdn-fileserver
861
date
Thu, 15 May 2025 10:03:10 GMT
cdn-storageserver
DE-635
last-modified
Mon, 12 May 2025 11:55:09 GMT
content-type
text/css
vary
Accept-Encoding
cdn-cache
HIT
access-control-allow-headers
Request-Id, Server, x-goog-meta-frames, Content-Length, Content-Type, Range, X-Requested-With, If-Modified-Since, If-None-Match, traceparent
cdn-requestpullcode
200
cdn-cachedat
05/12/2025 11:55:10
cache-control
public, max-age=31919000
cdn-requestpullsuccess
True
visitor-location
PT
cdn-requesttime
0
cdn-uid
d602dab6-3f92-4809-a378-608fd2b89403
cdn-requestid
fa562c0c9e549e39e1c63da1ee86415d
cdn-pullzone
236985
cdn-proxyver
1.27
access-control-allow-origin
*
cdn-edgestorageid
1082
server
Cookie First CDN-DE1-1079
cdn-requestcountrycode
PT
GET
H2
200
441.d794.c.js Show response
consent.cookiefirst.com/banner/v2.15.9/static-main-no-autoblock/
15 KB
7 KB
101ms
99ms
Script
application/javascript
169.150.247.36
CDN77 Datacamp Li...
General
Full URL
https://consent.cookiefirst.com/banner/v2.15.9/static-main-no-autoblock/441.d794.c.js
Requested by
Host: consent.cookiefirst.com
URL: https://consent.cookiefirst.com/banner.no-autoblock.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
169.150.247.36 Frankfurt am Main, Germany, ASN60068 (CDN77 Datacamp Limited, GB),
Reverse DNS
169-150-247-36.bunnyinfra.net
Software
Cookie First CDN-DE1-1079 /
Resource Hash
b3c5626f31221e5785725f4f4ff261565eb5f25b4377961ce9adc2616d20cfb3

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

cdn-status
200
access-control-expose-headers
Server, x-goog-meta-frames, Content-Length, Content-Type, Range, X-Requested-With, If-Modified-Since, If-None-Match, visitor-location
content-encoding
zstd
etag
"6821e19d-3b0d"
cdn-fileserver
861
date
Thu, 15 May 2025 10:03:10 GMT
cdn-storageserver
DE-677
last-modified
Mon, 12 May 2025 11:55:09 GMT
content-type
application/javascript
vary
Accept-Encoding
cdn-cache
HIT
access-control-allow-headers
Request-Id, Server, x-goog-meta-frames, Content-Length, Content-Type, Range, X-Requested-With, If-Modified-Since, If-None-Match, traceparent
cdn-requestpullcode
200
cdn-cachedat
05/12/2025 11:55:10
cache-control
public, max-age=31919000
cdn-requestpullsuccess
True
visitor-location
PT
cdn-requesttime
0
cdn-uid
d602dab6-3f92-4809-a378-608fd2b89403
cdn-requestid
8769452b6f5972082c7c533830cc98c9
cdn-pullzone
236985
cdn-proxyver
1.27
access-control-allow-origin
*
cdn-edgestorageid
1080
server
Cookie First CDN-DE1-1079
cdn-requestcountrycode
PT
GET
H2
200
ui.6ae9.c.css
consent.cookiefirst.com/banner/v2.15.9/static-main-no-autoblock/
16 KB
6 KB
84ms
83ms
Stylesheet
text/css
169.150.247.36
CDN77 Datacamp Li...
General
Full URL
https://consent.cookiefirst.com/banner/v2.15.9/static-main-no-autoblock/ui.6ae9.c.css
Requested by
Host: consent.cookiefirst.com
URL: https://consent.cookiefirst.com/banner.no-autoblock.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
169.150.247.36 Frankfurt am Main, Germany, ASN60068 (CDN77 Datacamp Limited, GB),
Reverse DNS
169-150-247-36.bunnyinfra.net
Software
Cookie First CDN-DE1-1079 /
Resource Hash
141e047935b2321d0c8a17e76f4a78eba0aadda8af0ef27fb5bd6b905ddb0b3d

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

cdn-status
200
access-control-expose-headers
Server, x-goog-meta-frames, Content-Length, Content-Type, Range, X-Requested-With, If-Modified-Since, If-None-Match, visitor-location
content-encoding
zstd
etag
"6821e19c-4038"
cdn-fileserver
862
date
Thu, 15 May 2025 10:03:10 GMT
cdn-storageserver
DE-638
last-modified
Mon, 12 May 2025 11:55:08 GMT
content-type
text/css
vary
Accept-Encoding
cdn-cache
HIT
access-control-allow-headers
Request-Id, Server, x-goog-meta-frames, Content-Length, Content-Type, Range, X-Requested-With, If-Modified-Since, If-None-Match, traceparent
cdn-requestpullcode
200
cdn-cachedat
05/12/2025 11:55:10
cache-control
public, max-age=31919000
cdn-requestpullsuccess
True
visitor-location
PT
cdn-requesttime
0
cdn-uid
d602dab6-3f92-4809-a378-608fd2b89403
cdn-requestid
72cb22c12b82df790a40f59677429cb0
cdn-pullzone
236985
cdn-proxyver
1.27
access-control-allow-origin
*
cdn-edgestorageid
1082
server
Cookie First CDN-DE1-1079
cdn-requestcountrycode
PT
GET
H2
200
ui.40dc.c.js Show response
consent.cookiefirst.com/banner/v2.15.9/static-main-no-autoblock/
46 KB
17 KB
89ms
88ms
Script
application/javascript
169.150.247.36
CDN77 Datacamp Li...
General
Full URL
https://consent.cookiefirst.com/banner/v2.15.9/static-main-no-autoblock/ui.40dc.c.js
Requested by
Host: consent.cookiefirst.com
URL: https://consent.cookiefirst.com/banner.no-autoblock.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
169.150.247.36 Frankfurt am Main, Germany, ASN60068 (CDN77 Datacamp Limited, GB),
Reverse DNS
169-150-247-36.bunnyinfra.net
Software
Cookie First CDN-DE1-1079 /
Resource Hash
f7199759c3dad40cc08d883170d02d116a713e97bfdb9fc207d3fd50c1222506

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

cdn-status
200
access-control-expose-headers
Server, x-goog-meta-frames, Content-Length, Content-Type, Range, X-Requested-With, If-Modified-Since, If-None-Match, visitor-location
content-encoding
zstd
etag
"6821e19c-b96d"
cdn-fileserver
383
date
Thu, 15 May 2025 10:03:10 GMT
cdn-storageserver
DE-633
last-modified
Mon, 12 May 2025 11:55:08 GMT
content-type
application/javascript
vary
Accept-Encoding
cdn-cache
HIT
access-control-allow-headers
Request-Id, Server, x-goog-meta-frames, Content-Length, Content-Type, Range, X-Requested-With, If-Modified-Since, If-None-Match, traceparent
cdn-requestpullcode
200
cdn-cachedat
05/12/2025 11:55:10
cache-control
public, max-age=31919000
cdn-requestpullsuccess
True
visitor-location
PT
cdn-requesttime
0
cdn-uid
d602dab6-3f92-4809-a378-608fd2b89403
cdn-requestid
98318f8b974add1dec1884184c861f54
cdn-pullzone
236985
cdn-proxyver
1.27
access-control-allow-origin
*
cdn-edgestorageid
1081
server
Cookie First CDN-DE1-1079
cdn-requestcountrycode
PT
GET
H2
200
560.362b.c.css
consent.cookiefirst.com/banner/v2.15.9/static-main-no-autoblock/
127 B
862 B
94ms
92ms
Stylesheet
text/css
169.150.247.36
CDN77 Datacamp Li...
General
Full URL
https://consent.cookiefirst.com/banner/v2.15.9/static-main-no-autoblock/560.362b.c.css
Requested by
Host: consent.cookiefirst.com
URL: https://consent.cookiefirst.com/banner.no-autoblock.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
169.150.247.36 Frankfurt am Main, Germany, ASN60068 (CDN77 Datacamp Limited, GB),
Reverse DNS
169-150-247-36.bunnyinfra.net
Software
Cookie First CDN-DE1-1079 /
Resource Hash
e7902b56545718b3f9dcc015b4acab60270239d559b0adaae9e5c81dd95a89a1

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

cdn-status
200
access-control-expose-headers
Server, x-goog-meta-frames, Content-Length, Content-Type, Range, X-Requested-With, If-Modified-Since, If-None-Match, visitor-location
content-encoding
zstd
etag
"6821e19d-7f"
cdn-fileserver
861
date
Thu, 15 May 2025 10:03:10 GMT
cdn-storageserver
DE-587
last-modified
Mon, 12 May 2025 11:55:09 GMT
content-type
text/css
vary
Accept-Encoding
cdn-cache
HIT
access-control-allow-headers
Request-Id, Server, x-goog-meta-frames, Content-Length, Content-Type, Range, X-Requested-With, If-Modified-Since, If-None-Match, traceparent
cdn-requestpullcode
200
cdn-cachedat
05/12/2025 11:55:10
cache-control
public, max-age=31919000
cdn-requestpullsuccess
True
visitor-location
PT
cdn-requesttime
0
cdn-uid
d602dab6-3f92-4809-a378-608fd2b89403
cdn-requestid
e37fc73271073899ef416238006dc0a7
cdn-pullzone
236985
cdn-proxyver
1.27
access-control-allow-origin
*
cdn-edgestorageid
1080
server
Cookie First CDN-DE1-1079
cdn-requestcountrycode
PT
GET
H2
200
560.52b6.c.js Show response
consent.cookiefirst.com/banner/v2.15.9/static-main-no-autoblock/
96 B
880 B
97ms
96ms
Script
application/javascript
169.150.247.36
CDN77 Datacamp Li...
General
Full URL
https://consent.cookiefirst.com/banner/v2.15.9/static-main-no-autoblock/560.52b6.c.js
Requested by
Host: consent.cookiefirst.com
URL: https://consent.cookiefirst.com/banner.no-autoblock.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
169.150.247.36 Frankfurt am Main, Germany, ASN60068 (CDN77 Datacamp Limited, GB),
Reverse DNS
169-150-247-36.bunnyinfra.net
Software
Cookie First CDN-DE1-1079 /
Resource Hash
6c726f6d1377f7bc870d49c8f6c323e9a52e35caff10b8a54e04b565c471d60f

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

cdn-status
200
access-control-expose-headers
Server, x-goog-meta-frames, Content-Length, Content-Type, Range, X-Requested-With, If-Modified-Since, If-None-Match, visitor-location
content-encoding
zstd
etag
"6821e19d-60"
cdn-fileserver
383
date
Thu, 15 May 2025 10:03:10 GMT
cdn-storageserver
DE-1019
last-modified
Mon, 12 May 2025 11:55:09 GMT
content-type
application/javascript
vary
Accept-Encoding
cdn-cache
HIT
access-control-allow-headers
Request-Id, Server, x-goog-meta-frames, Content-Length, Content-Type, Range, X-Requested-With, If-Modified-Since, If-None-Match, traceparent
cdn-requestpullcode
200
cdn-cachedat
05/12/2025 11:55:10
cache-control
public, max-age=31919000
cdn-requestpullsuccess
True
visitor-location
PT
cdn-requesttime
0
cdn-uid
d602dab6-3f92-4809-a378-608fd2b89403
cdn-requestid
ef8a5ee8b8654d7b08220ad6104943f9
cdn-pullzone
236985
cdn-proxyver
1.27
access-control-allow-origin
*
cdn-edgestorageid
1081
server
Cookie First CDN-DE1-1079
cdn-requestcountrycode
PT
GET
H2
200
css
fonts.googleapis.com/
17 KB
2 KB
94ms
93ms
Stylesheet
text/css
142.250.184.202
GOOGLE
General
Full URL
https://fonts.googleapis.com/css?family=Open%20Sans:400,b,i
Requested by
Host: static.elfsight.com
URL: https://static.elfsight.com/apps/form-builder/stable/274292b12c2c7489e79d9a0da37845f9c90336c2/app/formBuilder.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.250.184.202 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
fra24s11-in-f10.1e100.net
Software
ESF /
Resource Hash
ce33194867312cfba76a4d9c6525a906ad8f3562b70a95e4175fc8a67b54e2d1
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

content-encoding
gzip
x-content-type-options
nosniff
expires
Thu, 15 May 2025 10:03:11 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 15 May 2025 10:03:11 GMT
content-type
text/css; charset=utf-8
vary
Sec-Fetch-Dest, Sec-Fetch-Mode, Sec-Fetch-Site
last-modified
Thu, 15 May 2025 10:03:11 GMT
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=31536000
link
<https://fonts.gstatic.com>; rel=preconnect; crossorigin
cache-control
private, max-age=86400, stale-while-revalidate=604800
timing-allow-origin
*
cross-origin-opener-policy
same-origin-allow-popups
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
x-xss-protection
0
server
ESF
GET
H2
200
en-us-json-4138c17.js Show response
static.zdassets.com/web_widget/classic/latest/web-widget-locales/classic/ Frame 65CC
25 KB
6 KB
73ms
72ms
Script
application/javascript
216.198.54.3
CLOUDFLARESPECTRU...
General
Full URL
https://static.zdassets.com/web_widget/classic/latest/web-widget-locales/classic/en-us-json-4138c17.js
Requested by
Host: static.zdassets.com
URL: https://static.zdassets.com/web_widget/classic/latest/web-widget-main-4138c17.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
216.198.54.3 , United States, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
b87b92cd9b2943bcc97a64011eb833ef4205009327eaffe17db1cd001ae9ecc8
Security Headers
Name Value
Strict-Transport-Security max-age=0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

access-control-max-age
0
content-encoding
br
cf-cache-status
HIT
etag
W/"ef48436bf7997a9fed0856cd3df28c0f"
x-amz-version-id
JSk1VUmZkogk3hFEpRe8fPorAKvcBYW8
age
49059
report-to
{"endpoints":[{"url":"https:\/\/a.nel.cloudflare.com\/report\/v4?s=JeNnyR7oUffCpHcXGeUHKBgqNuJvx0cpeQ0Nis1QlHrVW92esgdjxI3LYxKsQ8lJRRKCbx68%2B%2BIA1VqsoKwITqM1lSQEB0QaC0N206oW%2FjBR3sP1EPrF5PBp9hsU4%2BoQKY29ZD4%3D"}],"group":"cf-nel","max_age":604800}
access-control-allow-methods
GET, HEAD
expires
Thu, 30 Apr 2026 14:47:37 GMT
date
Thu, 15 May 2025 10:03:11 GMT
content-type
application/javascript; charset=utf-8
last-modified
Wed, 30 Apr 2025 14:47:38 GMT
vary
Accept-Encoding
x-amz-id-2
+kT1oRIWGsxx6aCyIDvgnh8JZSCApYU1b04Qefz0HAbIWhK2TC05QJlI4FaL5g5PMf1UPrXQc88=
access-control-allow-headers
*
strict-transport-security
max-age=0
x-amz-replication-status
COMPLETED
cache-control
public, max-age=31536000
nel
{"success_fraction":0,"report_to":"cf-nel","max_age":604800}
x-amz-request-id
EQ4GW52VGSAKNF21
cf-ray
9401cdd41d5194ef-LIS
access-control-allow-origin
*
server
cloudflare
x-amz-server-side-encryption
AES256
GET
H2
200
config Show response
vsrevogroup.zendesk.com/embeddable/ Frame 65CC
593 B
1 KB
228ms
99ms
Fetch
application/json
216.198.54.1
CLOUDFLARESPECTRU...
General
Full URL
https://vsrevogroup.zendesk.com/embeddable/config
Requested by
Host: static.zdassets.com
URL: https://static.zdassets.com/web_widget/classic/latest/web-widget-main-4138c17.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
216.198.54.1 , United States, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
07fb86f93b0017be8ade6eea3eac28f6178b2df898fe5f644996674a5a58ca78

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

access-control-max-age
7200
x-request-id
9401cce44874ed08-AMS
access-control-expose-headers
x-zendesk-origin-server
embeddable-app-server-79b6f89d79-xpthm
content-encoding
gzip
cf-cache-status
HIT
report-to
{"endpoints":[{"url":"https:\/\/a.nel.cloudflare.com\/report\/v4?s=V%2BLTgRNn7igS8%2BUzubcI0K8cZ0Du34CR57UC%2BZ%2BBwJOh82TpuPBFjoI0E86oVNieozC4xFX7w3FiGPMK0e7u5MaFP%2FesS6JDlyLisbxfAq%2B1oyhjy%2Bw2Umvk03PEz9jIoFmmZ%2BczHQUE"}],"group":"cf-nel","max_age":604800}
access-control-allow-methods
GET
date
Thu, 15 May 2025 10:03:11 GMT
content-type
application/json; charset=utf-8
vary
Origin, Accept-Encoding
x-runtime
0.002565
last-modified
Thu, 15 May 2025 10:02:33 GMT
x-cache-status
HIT
cache-control
public, max-age=60, stale-while-revalidate=600, stale-if-error=3600
zendesk-service
embeddable
nel
{"success_fraction":0.01,"report_to":"cf-nel","max_age":604800}
x-envoy-upstream-service-time
7
x-envoy-decorator-operation
/embeddable
via
zorg
cf-ray
9401cdd4d9558e38-LIS
access-control-allow-origin
*
x-zendesk-zorg
yes
server
cloudflare
GET
H3
200
memQYaGs126MiZpBA-UFUIcVXSCEkx2cmqvXlWq8tWZ0Pw86hd0Rk8ZkWVAewA.woff2
fonts.gstatic.com/s/opensans/v40/
19 KB
19 KB
76ms
75ms
Font
font/woff2
216.58.206.35
GOOGLE
General
Full URL
https://fonts.gstatic.com/s/opensans/v40/memQYaGs126MiZpBA-UFUIcVXSCEkx2cmqvXlWq8tWZ0Pw86hd0Rk8ZkWVAewA.woff2
Requested by
Host: fonts.googleapis.com
URL: https://fonts.googleapis.com/css?family=Open%20Sans:400,b,i
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
216.58.206.35 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
lcfraa-aa-in-f3.1e100.net
Software
sffe /
Resource Hash
b4855cc8ec721cbaf27f3c907345e101b1524858221c14faa79df34cb2f84991
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Origin
https://www.revouninstaller.com
Referer
https://fonts.googleapis.com/

Response headers

age
140703
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Wed, 13 May 2026 18:58:08 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Tue, 13 May 2025 18:58:08 GMT
last-modified
Thu, 14 Dec 2023 02:02:23 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
19280
x-xss-protection
0
server
sffe
GET
H3
200
/
www.facebook.com/privacy_sandbox/topics/registration/
67 B
0
216ms
115ms
Fetch
image/png
157.240.252.35
FACEBOOK
General
Full URL
https://www.facebook.com/privacy_sandbox/topics/registration/?id=502397613272382
Requested by
Host: connect.facebook.net
URL: https://connect.facebook.net/signals/config/502397613272382?v=2.9.201&r=stable&domain=www.revouninstaller.com&hme=9ebdfdd473ffce6bfe2267012c83f73483198ffe20d84139a2066b7682f827c0&ex_m=73%2C128%2C113%2C117%2C64%2C6%2C106%2C72%2C19%2C100%2C92%2C54%2C57%2C181%2C202%2C209%2C205%2C206%2C208%2C32%2C107%2C56%2C80%2C207%2C176%2C179%2C203%2C204%2C189%2C139%2C44%2C194%2C191%2C192%2C37%2C151%2C18%2C53%2C198%2C197%2C141%2C21%2C43%2C2%2C46%2C68%2C69%2C70%2C74%2C96%2C20%2C17%2C99%2C95%2C94%2C114%2C55%2C116%2C42%2C115%2C33%2C97%2C29%2C177%2C180%2C148%2C14%2C15%2C16%2C8%2C9%2C28%2C25%2C26%2C60%2C65%2C67%2C78%2C105%2C108%2C30%2C79%2C12%2C10%2C83%2C51%2C24%2C110%2C109%2C111%2C102%2C13%2C23%2C4%2C41%2C77%2C22%2C160%2C89%2C135%2C76%2C1%2C98%2C59%2C87%2C36%2C31%2C85%2C86%2C91%2C40%2C7%2C93%2C84%2C47%2C35%2C38%2C0%2C71%2C118%2C90%2C5%2C50%2C49%2C101%2C88%2C246%2C174%2C126%2C163%2C156%2C3%2C39%2C66%2C45%2C112%2C48%2C82%2C63%2C62%2C34%2C103%2C61%2C58%2C52%2C81%2C75%2C27%2C104%2C11%2C119
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
157.240.252.35 Frankfurt am Main, Germany, ASN32934 (FACEBOOK, US),
Reverse DNS
edge-star-mini-shv-01-fra3.facebook.com
Software
/
Resource Hash
Security Headers
Name Value
Content-Security-Policy default-src blob: 'self' https://*.fbsbx.com *.facebook.com *.fbcdn.net;script-src *.facebook.com *.fbcdn.net *.facebook.net 127.0.0.1:* 'nonce-OsvhLORf' blob: data: 'self' connect.facebook.net 'wasm-unsafe-eval' https://*.google-analytics.com *.google.com;style-src *.fbcdn.net data: *.facebook.com 'unsafe-inline' https://fonts.googleapis.com;connect-src *.facebook.com facebook.com *.fbcdn.net *.facebook.net wss://*.facebook.com:* wss://*.whatsapp.com:* wss://*.fbcdn.net attachment.fbsbx.com ws://localhost:* blob: *.cdninstagram.com 'self' http://localhost:3103 wss://gateway.facebook.com wss://edge-chat.facebook.com wss://snaptu-d.facebook.com wss://kaios-d.facebook.com/ v.whatsapp.net *.fbsbx.com *.fb.com https://*.google-analytics.com;font-src data: *.facebook.com *.fbcdn.net *.fbsbx.com https://fonts.gstatic.com;img-src *.fbcdn.net *.facebook.com data: https://*.fbsbx.com facebook.com *.cdninstagram.com fbsbx.com fbcdn.net connect.facebook.net *.carriersignal.info blob: android-webview-video-poster: *.whatsapp.net *.fb.com *.oculuscdn.com *.tenor.co *.tenor.com *.giphy.com https://paywithmybank.com/ https://*.paywithmybank.com/ https://www.googleadservices.com https://googleads.g.doubleclick.net https://*.google-analytics.com;media-src *.cdninstagram.com blob: *.fbcdn.net *.fbsbx.com www.facebook.com *.facebook.com data: *.tenor.co *.tenor.com https://*.giphy.com;child-src data: blob: 'self' https://*.fbsbx.com *.facebook.com *.fbcdn.net;frame-src *.facebook.com *.fbsbx.com fbsbx.com data: www.instagram.com *.fbcdn.net accounts.meta.com https://paywithmybank.com/ https://*.paywithmybank.com/ https://www.googleadservices.com https://googleads.g.doubleclick.net https://www.google.com https://td.doubleclick.net *.google.com *.doubleclick.net;manifest-src data: blob: 'self' https://*.fbsbx.com *.facebook.com *.fbcdn.net;object-src data: blob: 'self' https://*.fbsbx.com *.facebook.com *.fbcdn.net;worker-src blob: *.facebook.com data:;block-all-mixed-content;upgrade-insecure-requests;
Strict-Transport-Security max-age=15552000; preload
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

access-control-expose-headers
X-FB-Debug, X-Loader-Length, X-Stack, Error-MID
content-encoding
zstd
report-to
{"max_age":2592000,"endpoints":[{"url":"https:\/\/www.facebook.com\/browser_reporting\/coop\/?minimize=0"}],"group":"coop_report","include_subdomains":true}, {"max_age":259200,"endpoints":[{"url":"https:\/\/www.facebook.com\/ajax\/browser_error_reports\/?device_level=unknown&brsid=7504610921327006369&cpp=C3&cv=1022865115&st=1747303391544"}]}, {"max_age":21600,"endpoints":[{"url":"https:\/\/www.facebook.com\/ajax\/browser_error_reports\/"}],"group":"permissions_policy"}
x-content-type-options
nosniff
observe-browsing-topics
?1
expires
Sat, 01 Jan 2000 00:00:00 GMT
access-control-allow-methods
OPTIONS
alt-svc
h3=":443"; ma=86400
date
Thu, 15 May 2025 10:03:11 GMT
content-type
image/png
vary
Origin, Accept-Encoding
x-fb-debug
rHzm/w/8ksM8p/zaCf32WkysRHyt89uC1aew8/5rOKvKEXIJWyx16dHn7pKlSAwFizefo8BtBo1f/F3NN4Eq3g==
priority
u=1,i
strict-transport-security
max-age=15552000; preload
reporting-endpoints
coop_report="https://www.facebook.com/browser_reporting/coop/?minimize=0", default="https://www.facebook.com/ajax/browser_error_reports/?device_level=unknown&brsid=7504610921327006369&cpp=C3&cv=1022865115&st=1747303391544", permissions_policy="https://www.facebook.com/ajax/browser_error_reports/"
content-security-policy
default-src blob: 'self' https://*.fbsbx.com *.facebook.com *.fbcdn.net;script-src *.facebook.com *.fbcdn.net *.facebook.net 127.0.0.1:* 'nonce-OsvhLORf' blob: data: 'self' connect.facebook.net 'wasm-unsafe-eval' https://*.google-analytics.com *.google.com;style-src *.fbcdn.net data: *.facebook.com 'unsafe-inline' https://fonts.googleapis.com;connect-src *.facebook.com facebook.com *.fbcdn.net *.facebook.net wss://*.facebook.com:* wss://*.whatsapp.com:* wss://*.fbcdn.net attachment.fbsbx.com ws://localhost:* blob: *.cdninstagram.com 'self' http://localhost:3103 wss://gateway.facebook.com wss://edge-chat.facebook.com wss://snaptu-d.facebook.com wss://kaios-d.facebook.com/ v.whatsapp.net *.fbsbx.com *.fb.com https://*.google-analytics.com;font-src data: *.facebook.com *.fbcdn.net *.fbsbx.com https://fonts.gstatic.com;img-src *.fbcdn.net *.facebook.com data: https://*.fbsbx.com facebook.com *.cdninstagram.com fbsbx.com fbcdn.net connect.facebook.net *.carriersignal.info blob: android-webview-video-poster: *.whatsapp.net *.fb.com *.oculuscdn.com *.tenor.co *.tenor.com *.giphy.com https://paywithmybank.com/ https://*.paywithmybank.com/ https://www.googleadservices.com https://googleads.g.doubleclick.net https://*.google-analytics.com;media-src *.cdninstagram.com blob: *.fbcdn.net *.fbsbx.com www.facebook.com *.facebook.com data: *.tenor.co *.tenor.com https://*.giphy.com;child-src data: blob: 'self' https://*.fbsbx.com *.facebook.com *.fbcdn.net;frame-src *.facebook.com *.fbsbx.com fbsbx.com data: www.instagram.com *.fbcdn.net accounts.meta.com https://paywithmybank.com/ https://*.paywithmybank.com/ https://www.googleadservices.com https://googleads.g.doubleclick.net https://www.google.com https://td.doubleclick.net *.google.com *.doubleclick.net;manifest-src data: blob: 'self' https://*.fbsbx.com *.facebook.com *.fbcdn.net;object-src data: blob: 'self' https://*.fbsbx.com *.facebook.com *.fbcdn.net;worker-src blob: *.facebook.com data:;block-all-mixed-content;upgrade-insecure-requests;
cache-control
private, no-store, no-cache, must-revalidate
x-fb-connection-quality
GOOD; q=0.7, rtt=77, rtx=0, c=23, mss=1232, tbw=4808, tp=9, tpl=0, uplat=36, ullat=0
cross-origin-opener-policy
same-origin-allow-popups;report-to="coop_report"
pragma
no-cache
cross-origin-resource-policy
same-origin
access-control-allow-credentials
true
permissions-policy
accelerometer=(), attribution-reporting=(self), autoplay=(), bluetooth=(), browsing-topics=(self), camera=(self), ch-device-memory=(), ch-downlink=(), ch-dpr=(), ch-ect=(), ch-rtt=(), ch-save-data=(), ch-ua-arch=(), ch-ua-bitness=(), ch-viewport-height=(), ch-viewport-width=(), ch-width=(), clipboard-read=(self), clipboard-write=(self), compute-pressure=(), display-capture=(self), encrypted-media=(self), fullscreen=(self), gamepad=*, geolocation=(self), gyroscope=(), hid=(), idle-detection=(), interest-cohort=(self), keyboard-map=(), local-fonts=(), magnetometer=(), microphone=(self), midi=(), otp-credentials=(), payment=(), picture-in-picture=(self), private-state-token-issuance=(), publickey-credentials-get=(self), screen-wake-lock=(), serial=(), shared-storage=(), shared-storage-select-url=(), private-state-token-redemption=(), usb=(), unload=(self), window-management=(), xr-spatial-tracking=(self);report-to="permissions_policy"
document-policy
force-load-at-top
access-control-allow-origin
*
x-xss-protection
0
origin-agent-cluster
?1
GET
H3
200
/
www.facebook.com/tr/
0
19 B
174ms
83ms
Image
text/plain
157.240.252.35
FACEBOOK
General
Full URL
https://www.facebook.com/tr/?id=502397613272382&ev=PageView&dl=https%3A%2F%2Fwww.revouninstaller.com%2Ffree-install-thankyou%2F&rl=&if=false&ts=1747303391381&sw=1600&sh=1200&v=2.9.201&r=stable&a=tmgoogletagmanager&ec=0&o=12318&fbp=fb.1.1747303391377.567601859912204072&cs_est=true&ler=empty&cdl=API_unavailable&it=1747303390867&coo=false&exp=k2&rqm=GET
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
157.240.252.35 Frankfurt am Main, Germany, ASN32934 (FACEBOOK, US),
Reverse DNS
edge-star-mini-shv-01-fra3.facebook.com
Software
proxygen-bolt /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
x-fb-connection-quality
GOOD; q=0.7, rtt=76, rtx=0, c=23, mss=1232, tbw=4853, tp=10, tpl=0, uplat=0, ullat=0
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
access-control-allow-origin
alt-svc
h3=":443"; ma=86400
content-length
0
date
Thu, 15 May 2025 10:03:11 GMT
content-type
text/plain
server
proxygen-bolt
priority
u=3,i
GET
H3
200
/
www.facebook.com/privacy_sandbox/pixel/register/trigger/
67 B
200 B
355ms
265ms
Image
image/png
157.240.252.35
FACEBOOK
General
Full URL
https://www.facebook.com/privacy_sandbox/pixel/register/trigger/?id=502397613272382&ev=PageView&dl=https%3A%2F%2Fwww.revouninstaller.com%2Ffree-install-thankyou%2F&rl=&if=false&ts=1747303391381&sw=1600&sh=1200&v=2.9.201&r=stable&a=tmgoogletagmanager&ec=0&o=12318&fbp=fb.1.1747303391377.567601859912204072&cs_est=true&ler=empty&cdl=API_unavailable&it=1747303390867&coo=false&exp=k2&rqm=FGET
Requested by
Host: www.revouninstaller.com
URL: https://www.revouninstaller.com/free-install-thankyou/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
157.240.252.35 Frankfurt am Main, Germany, ASN32934 (FACEBOOK, US),
Reverse DNS
edge-star-mini-shv-01-fra3.facebook.com
Software
/
Resource Hash
aa7b6c81e85551eeb5c4809f1e683efa0b780c33d12ddfc2067a1b136803e45a
Security Headers
Name Value
Content-Security-Policy default-src blob: 'self' https://*.fbsbx.com *.facebook.com *.fbcdn.net;script-src *.facebook.com *.fbcdn.net *.facebook.net 127.0.0.1:* 'nonce-ft48czEA' blob: data: 'self' connect.facebook.net 'wasm-unsafe-eval' https://*.google-analytics.com *.google.com;style-src *.fbcdn.net data: *.facebook.com 'unsafe-inline' https://fonts.googleapis.com;connect-src *.facebook.com facebook.com *.fbcdn.net *.facebook.net wss://*.facebook.com:* wss://*.whatsapp.com:* wss://*.fbcdn.net attachment.fbsbx.com ws://localhost:* blob: *.cdninstagram.com 'self' http://localhost:3103 wss://gateway.facebook.com wss://edge-chat.facebook.com wss://snaptu-d.facebook.com wss://kaios-d.facebook.com/ v.whatsapp.net *.fbsbx.com *.fb.com https://*.google-analytics.com;font-src data: *.facebook.com *.fbcdn.net *.fbsbx.com https://fonts.gstatic.com;img-src *.fbcdn.net *.facebook.com data: https://*.fbsbx.com facebook.com *.cdninstagram.com fbsbx.com fbcdn.net connect.facebook.net *.carriersignal.info blob: android-webview-video-poster: *.whatsapp.net *.fb.com *.oculuscdn.com *.tenor.co *.tenor.com *.giphy.com https://paywithmybank.com/ https://*.paywithmybank.com/ https://www.googleadservices.com https://googleads.g.doubleclick.net https://*.google-analytics.com;media-src *.cdninstagram.com blob: *.fbcdn.net *.fbsbx.com www.facebook.com *.facebook.com data: *.tenor.co *.tenor.com https://*.giphy.com;child-src data: blob: 'self' https://*.fbsbx.com *.facebook.com *.fbcdn.net;frame-src *.facebook.com *.fbsbx.com fbsbx.com data: www.instagram.com *.fbcdn.net accounts.meta.com https://paywithmybank.com/ https://*.paywithmybank.com/ https://www.googleadservices.com https://googleads.g.doubleclick.net https://www.google.com https://td.doubleclick.net *.google.com *.doubleclick.net;manifest-src data: blob: 'self' https://*.fbsbx.com *.facebook.com *.fbcdn.net;object-src data: blob: 'self' https://*.fbsbx.com *.facebook.com *.fbcdn.net;worker-src blob: *.facebook.com data:;block-all-mixed-content;upgrade-insecure-requests;
Strict-Transport-Security max-age=15552000; preload
X-Content-Type-Options nosniff
X-Frame-Options DENY
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

content-encoding
zstd
report-to
{"max_age":2592000,"endpoints":[{"url":"https:\/\/www.facebook.com\/browser_reporting\/coop\/?minimize=0"}],"group":"coop_report","include_subdomains":true}, {"max_age":86400,"endpoints":[{"url":"https:\/\/www.facebook.com\/browser_reporting\/coep\/?minimize=0"}],"group":"coep_report"}, {"max_age":259200,"endpoints":[{"url":"https:\/\/www.facebook.com\/ajax\/browser_error_reports\/?device_level=unknown&brsid=7504610920934432522&cpp=C3&cv=1022865115&st=1747303391543"}]}, {"max_age":21600,"endpoints":[{"url":"https:\/\/www.facebook.com\/ajax\/browser_error_reports\/"}],"group":"permissions_policy"}
x-content-type-options
nosniff
expires
Sat, 01 Jan 2000 00:00:00 GMT
alt-svc
h3=":443"; ma=86400
date
Thu, 15 May 2025 10:03:11 GMT
content-type
image/png
vary
Accept-Encoding
cross-origin-embedder-policy-report-only
require-corp;report-to="coep_report"
priority
u=3,i
x-frame-options
DENY
strict-transport-security
max-age=15552000; preload
reporting-endpoints
coop_report="https://www.facebook.com/browser_reporting/coop/?minimize=0", coep_report="https://www.facebook.com/browser_reporting/coep/?minimize=0", default="https://www.facebook.com/ajax/browser_error_reports/?device_level=unknown&brsid=7504610920934432522&cpp=C3&cv=1022865115&st=1747303391543", permissions_policy="https://www.facebook.com/ajax/browser_error_reports/"
content-security-policy
default-src blob: 'self' https://*.fbsbx.com *.facebook.com *.fbcdn.net;script-src *.facebook.com *.fbcdn.net *.facebook.net 127.0.0.1:* 'nonce-ft48czEA' blob: data: 'self' connect.facebook.net 'wasm-unsafe-eval' https://*.google-analytics.com *.google.com;style-src *.fbcdn.net data: *.facebook.com 'unsafe-inline' https://fonts.googleapis.com;connect-src *.facebook.com facebook.com *.fbcdn.net *.facebook.net wss://*.facebook.com:* wss://*.whatsapp.com:* wss://*.fbcdn.net attachment.fbsbx.com ws://localhost:* blob: *.cdninstagram.com 'self' http://localhost:3103 wss://gateway.facebook.com wss://edge-chat.facebook.com wss://snaptu-d.facebook.com wss://kaios-d.facebook.com/ v.whatsapp.net *.fbsbx.com *.fb.com https://*.google-analytics.com;font-src data: *.facebook.com *.fbcdn.net *.fbsbx.com https://fonts.gstatic.com;img-src *.fbcdn.net *.facebook.com data: https://*.fbsbx.com facebook.com *.cdninstagram.com fbsbx.com fbcdn.net connect.facebook.net *.carriersignal.info blob: android-webview-video-poster: *.whatsapp.net *.fb.com *.oculuscdn.com *.tenor.co *.tenor.com *.giphy.com https://paywithmybank.com/ https://*.paywithmybank.com/ https://www.googleadservices.com https://googleads.g.doubleclick.net https://*.google-analytics.com;media-src *.cdninstagram.com blob: *.fbcdn.net *.fbsbx.com www.facebook.com *.facebook.com data: *.tenor.co *.tenor.com https://*.giphy.com;child-src data: blob: 'self' https://*.fbsbx.com *.facebook.com *.fbcdn.net;frame-src *.facebook.com *.fbsbx.com fbsbx.com data: www.instagram.com *.fbcdn.net accounts.meta.com https://paywithmybank.com/ https://*.paywithmybank.com/ https://www.googleadservices.com https://googleads.g.doubleclick.net https://www.google.com https://td.doubleclick.net *.google.com *.doubleclick.net;manifest-src data: blob: 'self' https://*.fbsbx.com *.facebook.com *.fbcdn.net;object-src data: blob: 'self' https://*.fbsbx.com *.facebook.com *.fbcdn.net;worker-src blob: *.facebook.com data:;block-all-mixed-content;upgrade-insecure-requests;
cache-control
private, no-store, no-cache, must-revalidate
x-fb-debug
FCYN0EcXAOKxvdbG6tWBuVzd7zQnryXuzGvSiSG3/yox6EanpiZRfPcj+6SvqsUm2OEvJ1CN9UeNPHaubrbgGw==
cross-origin-opener-policy
same-origin-allow-popups
x-fb-connection-quality
GOOD; q=0.7, rtt=76, rtx=0, c=24, mss=1232, tbw=5221, tp=13, tpl=0, uplat=186, ullat=0
pragma
no-cache
cross-origin-resource-policy
cross-origin
permissions-policy
accelerometer=(), attribution-reporting=(self), autoplay=(), bluetooth=(), browsing-topics=(self), camera=(self), ch-device-memory=(), ch-downlink=(), ch-dpr=(), ch-ect=(), ch-rtt=(), ch-save-data=(), ch-ua-arch=(), ch-ua-bitness=(), ch-viewport-height=(), ch-viewport-width=(), ch-width=(), clipboard-read=(self), clipboard-write=(self), compute-pressure=(), display-capture=(self), encrypted-media=(self), fullscreen=(self), gamepad=*, geolocation=(self), gyroscope=(), hid=(), idle-detection=(), interest-cohort=(self), keyboard-map=(), local-fonts=(), magnetometer=(), microphone=(self), midi=(), otp-credentials=(), payment=(), picture-in-picture=(self), private-state-token-issuance=(), publickey-credentials-get=(self), screen-wake-lock=(), serial=(), shared-storage=(), shared-storage-select-url=(), private-state-token-redemption=(), usb=(), unload=(self), window-management=(), xr-spatial-tracking=(self);report-to="permissions_policy"
document-policy
force-load-at-top
cross-origin-opener-policy-report-only
restrict-properties;report-to="coop_report"
x-xss-protection
0
origin-agent-cluster
?1
GET
H2
200
styles.css Show response
consent.cookiefirst.com/sites/revouninstaller.com-eaf2c1f3-7cb1-4b17-9342-3053be0001d7/
2 KB
1 KB
90ms
89ms
Fetch
text/css
169.150.247.36
CDN77 Datacamp Li...
General
Full URL
https://consent.cookiefirst.com/sites/revouninstaller.com-eaf2c1f3-7cb1-4b17-9342-3053be0001d7/styles.css?v=7bd5a67b-168c-4f03-8306-4d32216ee01f
Requested by
Host: consent.cookiefirst.com
URL: https://consent.cookiefirst.com/banner.no-autoblock.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
169.150.247.36 Frankfurt am Main, Germany, ASN60068 (CDN77 Datacamp Limited, GB),
Reverse DNS
169-150-247-36.bunnyinfra.net
Software
Cookie First CDN-DE1-1079 /
Resource Hash
4921a0babdab48814eee76ca2b58b5b1b7dfb90e801db7aaad98230acfd9eb37

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

cdn-status
200
access-control-expose-headers
Server, x-goog-meta-frames, Content-Length, Content-Type, Range, X-Requested-With, If-Modified-Since, If-None-Match, visitor-location
content-encoding
zstd
etag
"6815ceb4-709"
cdn-fileserver
599
date
Thu, 15 May 2025 10:03:11 GMT
cdn-storageserver
DE-588
last-modified
Sat, 03 May 2025 08:07:16 GMT
content-type
text/css
vary
Accept-Encoding
cdn-cache
HIT
access-control-allow-headers
Request-Id, Server, x-goog-meta-frames, Content-Length, Content-Type, Range, X-Requested-With, If-Modified-Since, If-None-Match, traceparent
cdn-requestpullcode
200
cdn-cachedat
05/11/2025 21:02:43
cache-control
public, max-age=31919000
cdn-requestpullsuccess
True
visitor-location
PT
cdn-requesttime
0
cdn-uid
d602dab6-3f92-4809-a378-608fd2b89403
cdn-requestid
fd433cf11fee488dfee935e7d8762d28
cdn-pullzone
236985
cdn-proxyver
1.27
access-control-allow-origin
*
cdn-edgestorageid
1080
server
Cookie First CDN-DE1-1079
cdn-requestcountrycode
PT
GET
H2
200
web-widget-chat-sdk-4138c17.js Show response
static.zdassets.com/web_widget/classic/latest/ Frame 65CC
217 KB
54 KB
71ms
70ms
Script
application/javascript
216.198.54.3
CLOUDFLARESPECTRU...
General
Full URL
https://static.zdassets.com/web_widget/classic/latest/web-widget-chat-sdk-4138c17.js
Requested by
Host: static.zdassets.com
URL: https://static.zdassets.com/web_widget/classic/latest/web-widget-main-4138c17.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
216.198.54.3 , United States, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
f33c7bd75e8107b0e2c531d98af84d90780d913f9246e796ea633d948d91f709
Security Headers
Name Value
Strict-Transport-Security max-age=0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

access-control-max-age
0
content-encoding
br
cf-cache-status
HIT
etag
W/"08a68a7308737a004b2991aa3dd00688"
x-amz-version-id
oJtxclV33CZqbFO2Ogci7yAd8DIVuKab
age
1266535
report-to
{"endpoints":[{"url":"https:\/\/a.nel.cloudflare.com\/report\/v4?s=kCTMq8u5n40KMf5OmKJjsaD8xolcT2FiJMimqMqRZsV4x%2BlnyLcYRZsHQ58ECDteeEvBEXzBVOpM6bT0XPh1btb%2BFMxm%2F%2BEdQPXgOcWsanuXFpp2qmTtBMLMM8irC4WVLGepoqY%3D"}],"group":"cf-nel","max_age":604800}
access-control-allow-methods
GET, HEAD
expires
Thu, 30 Apr 2026 14:47:35 GMT
date
Thu, 15 May 2025 10:03:11 GMT
content-type
application/javascript; charset=utf-8
last-modified
Wed, 30 Apr 2025 14:47:36 GMT
vary
Accept-Encoding
x-amz-id-2
hW9fmd7SCD6UKiPXR1fzs3t2a9nKUqn0OX13TYQwg+ERxo9w7Qmb9X/6jpcMsP8a2EOQv1AiWvHyireXulzP9A==
access-control-allow-headers
*
strict-transport-security
max-age=0
x-amz-replication-status
COMPLETED
cache-control
public, max-age=31536000
nel
{"success_fraction":0,"report_to":"cf-nel","max_age":604800}
x-amz-request-id
EQ4WGQZPDFP8A652
cf-ray
9401cdd49e1794ef-LIS
access-control-allow-origin
*
server
cloudflare
x-amz-server-side-encryption
AES256
GET
H2
200
favicon.ico
www.revouninstaller.com/
2 KB
3 KB
143ms
142ms
Other
image/vnd.microsoft.icon
146.20.152.114
RACKSPACE
General
Full URL
https://www.revouninstaller.com/favicon.ico
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
146.20.152.114 , United States, ASN27357 (RACKSPACE, US),
Reverse DNS
1333686-web1.vsrevogroup.com
Software
XYZ /
Resource Hash
91e8f868eef6967dcfca5eeb8e428184a0f4dcd017246c78138e71e158a78db7
Security Headers
Name Value
Content-Security-Policy frame-ancestors 'self';
Strict-Transport-Security max-age=31536000; includeSubdomains
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 1; mode=block

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/free-install-thankyou/

Response headers

x-permitted-cross-domain-policies
none
x-content-type-options
nosniff
expires
max-age=A10368000, public
date
Thu, 15 May 2025 10:03:11 GMT
last-modified
Wed, 18 Mar 2020 08:36:11 GMT
content-type
image/vnd.microsoft.icon
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=31536000; includeSubdomains
content-security-policy
frame-ancestors 'self';
cache-control
max-age=31536000, public
referrer-policy
no-referrer, strict-origin-when-cross-origin
permissions-policy
interest-cohort=()
accept-ranges
bytes
content-length
2462
x-xss-protection
1; mode=block
server
XYZ
GET
H2
200
393O9gB158xzzs9O82F04ypD5NUqTehW-banner
v2assets.zopim.io/ Frame 9B2F
17 KB
18 KB
187ms
56ms
Image
image/png
104.16.200.19
CLOUDFLARENET
General
Full URL
https://v2assets.zopim.io/393O9gB158xzzs9O82F04ypD5NUqTehW-banner?1654172833774
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.16.200.19 -, , ASN13335 (CLOUDFLARENET, US),
Reverse DNS
Software
cloudflare /
Resource Hash
936cb6d96f115d51e7a2ac5aa09bb2c247a7daa04951ff4b82dd14518ff2e6af

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

x-robots-tag
none, noarchive
cache-control
public, max-age=86400
cf-cache-status
HIT
etag
"e8f01fc47e082b951fe241fd1a291696"
age
421741
cf-ray
9401cdd989bfe3b1-LIS
expires
Fri, 16 May 2025 10:03:12 GMT
accept-ranges
bytes
content-length
17708
date
Thu, 15 May 2025 10:03:12 GMT
content-type
image/png
last-modified
Thu, 02 Jun 2022 12:27:15 GMT
vary
Accept-Encoding
server
cloudflare
GET
H2
200
web-widget-chat-incoming-message-notification-4138c17.js Show response
static.zdassets.com/web_widget/classic/latest/ Frame 65CC
236 B
842 B
59ms
59ms
Script
application/javascript
216.198.54.3
CLOUDFLARESPECTRU...
General
Full URL
https://static.zdassets.com/web_widget/classic/latest/web-widget-chat-incoming-message-notification-4138c17.js
Requested by
Host: static.zdassets.com
URL: https://static.zdassets.com/web_widget/classic/latest/web-widget-main-4138c17.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
216.198.54.3 , United States, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
eb2902ff32366de00d3afa351aeceb1357d5a468eacbb2fd92cf115276d626cb
Security Headers
Name Value
Strict-Transport-Security max-age=0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer

Response headers

access-control-max-age
0
content-encoding
br
cf-cache-status
HIT
etag
W/"e9d8b92096016dfd74d2f2500556464e"
x-amz-version-id
dXd3_hyDug9PkA3xpn4iPojnpm2bGt18
age
1266535
report-to
{"endpoints":[{"url":"https:\/\/a.nel.cloudflare.com\/report\/v4?s=4JK%2FbvbqZ7b7oSWpPm3sUhl77zYmYd6V1ttCSq52VhQ4K2Y1ofyTU6y%2Fh%2Fu9Pxn9pPqZCbLWTdkvbpLx3P7BUJGoGyYAVnP%2BuAixPzeU%2BViC1WhBwSK%2Ffsn3BQJvy3iX%2FG0uN2U%3D"}],"group":"cf-nel","max_age":604800}
access-control-allow-methods
GET, HEAD
expires
Thu, 30 Apr 2026 14:47:35 GMT
date
Thu, 15 May 2025 10:03:12 GMT
content-type
application/javascript; charset=utf-8
last-modified
Wed, 30 Apr 2025 14:47:36 GMT
vary
Accept-Encoding
x-amz-id-2
xP6/YMXfp/LaBqb6/HCu60QkqIua7pEW4ellQHtCX8CpS8Dx/KT1nswTeZAdVxjdQ+Zz2UIG+Bw=
access-control-allow-headers
*
strict-transport-security
max-age=0
x-amz-replication-status
COMPLETED
cache-control
public, max-age=31536000
nel
{"success_fraction":0,"report_to":"cf-nel","max_age":604800}
x-amz-request-id
V9V2Q8GW0NPBCZXC
cf-ray
9401cdd8dc1694ef-LIS
access-control-allow-origin
*
server
cloudflare
x-amz-server-side-encryption
AES256
GET
H2
206
fda6cd35495c75f83508d9d2e77ee33d.mp3
static.zdassets.com/web_widget/classic/latest/ Frame 65CC
19 KB
20 KB
64ms
64ms
Media
audio/mpeg
216.198.54.3
CLOUDFLARESPECTRU...
General
Full URL
https://static.zdassets.com/web_widget/classic/latest/fda6cd35495c75f83508d9d2e77ee33d.mp3
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
216.198.54.3 , United States, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
05069cc62b394b6ecc2daf3c51b4b2ba7f6cc8735988e8234487234af47eceee
Security Headers
Name Value
Strict-Transport-Security max-age=0

Request headers

Referer
Accept-Encoding
identity;q=1, *;q=0
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Range
bytes=0-

Response headers

access-control-max-age
0
cf-cache-status
HIT
etag
"f11ce9e8f40a392830217253fe75d6de"
x-amz-version-id
SbGCIJ2SN2UNtezVUBsPz6twHS7ItMYi
age
1574805
report-to
{"endpoints":[{"url":"https:\/\/a.nel.cloudflare.com\/report\/v4?s=Uy%2F7Gov1tk52M6DGALm%2F1zuLg6sW%2F7eFoib5weDrw%2BCTNjej3yOTFPbWA1tUlQZdqQzXgLMNSoZc%2F8jFMppO7djk0FaOvjinJ6qc6tWaNuPYMfoT9Zh2YrHMklPx%2Fx4bJY%2B5N%2FM%3D"}],"group":"cf-nel","max_age":604800}
access-control-allow-methods
GET, HEAD
expires
Fri, 17 Apr 2026 12:38:06 GMT
date
Thu, 15 May 2025 10:03:12 GMT
content-type
audio/mpeg; charset=utf-8
last-modified
Fri, 27 Dec 2024 08:59:09 GMT
vary
Accept-Encoding
x-amz-id-2
EwJG3MvmG7Pkb5y9hUBk4MwamVqWrqiQe71DZz17bkR58PbYfvj3naftpBxvqzxSV4pbertktEmsnVOaCXKkjOjWGfPlrv1D
access-control-allow-headers
*
strict-transport-security
max-age=0
x-amz-replication-status
COMPLETED
cache-control
public, max-age=31536000
nel
{"success_fraction":0,"report_to":"cf-nel","max_age":604800}
Content-Range
bytes 0-19697/19698
x-amz-request-id
S86B5DGWRSV3981T
cf-ray
9401cdd94ca094ef-LIS
access-control-allow-origin
*
Content-Length
19698
server
cloudflare
x-amz-server-side-encryption
AES256
POST
H2
204
collect
region1.analytics.google.com/g/
0
0
199ms
73ms
Fetch
text/plain
216.239.34.36
GOOGLE
General
Full URL
https://region1.analytics.google.com/g/collect?v=2&tid=G-P73P80145H&gtm=45je55d1v869118035z871855269za200zb71855269&_p=1747303389200&_gaz=1&gcs=G111&gcd=13t3t3t2t5l1&npa=0&dma_cps=syphamo&dma=1&tag_exp=101509157~103116026~103130498~103130500~103200004~103207802~103233427~103252644~103252646~103263073~103301114~103301116&ptag_exp=101509157~103116026~103130498~103130500~103200004~103233427~103252644~103252646~103301114~103301116&cid=1371600675.1747303391&ul=pt-pt&sr=1600x1200&uaa=&uab=&uafvl=&uamb=0&uam=&uap=&uapv=&uaw=0&are=1&pae=1&frm=0&pscdl=noapi&_s=1&sid=1747303390&sct=1&seg=0&dl=https%3A%2F%2Fwww.revouninstaller.com%2Ffree-install-thankyou%2F&dt=Thank%20you%20for%20installing%20Revo%20Uninstaller%20Free&_tu=QA&en=page_view&_fv=1&_ss=1&tfd=4368
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtag/js?id=G-P73P80145H&cx=c&gtm=45He55d1v71855269za200&tag_exp=101509157~103116026~103130498~103130500~103200004~103233427~103252644~103252646~103301114~103301116
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
216.239.34.36 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
Software
Golfe2 /
Resource Hash

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

cache-control
no-cache, no-store, must-revalidate
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
content-security-policy-report-only
script-src 'none'; form-action 'none'; frame-src 'none'; report-uri https://csp.withgoogle.com/csp/scaffolding/ascnsrsggc:153:0
report-to
{"group":"ascnsrsggc:153:0","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/scaffolding/ascnsrsggc:153:0"}],}
expires
Fri, 01 Jan 1990 00:00:00 GMT
access-control-allow-origin
https://www.revouninstaller.com
cross-origin-opener-policy-report-only
same-origin; report-to=ascnsrsggc:153:0
content-length
0
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 15 May 2025 10:03:12 GMT
content-type
text/plain
server
Golfe2
POST
H2
204
collect
stats.g.doubleclick.net/g/
0
563 B
222ms
68ms
Ping
text/plain
142.251.168.154
GOOGLE
General
Full URL
https://stats.g.doubleclick.net/g/collect?v=2&tid=G-P73P80145H&cid=1371600675.1747303391&gtm=45je55d1v869118035z871855269za200zb71855269&aip=1&dma=1&dma_cps=syphamo&gcs=G111&gcd=13t3t3t2t5l1&npa=0&frm=0&tag_exp=101509157~103116026~103130498~103130500~103200004~103207802~103233427~103252644~103252646~103263073~103301114~103301116&ptag_exp=101509157~103116026~103130498~103130500~103200004~103233427~103252644~103252646~103301114~103301116
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtag/js?id=G-P73P80145H&cx=c&gtm=45He55d1v71855269za200&tag_exp=101509157~103116026~103130498~103130500~103200004~103233427~103252644~103252646~103301114~103301116
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.168.154 Farmingdale, United States, ASN15169 (GOOGLE, US),
Reverse DNS
wh-in-f154.1e100.net
Software
Golfe2 /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

cache-control
no-cache, no-store, must-revalidate
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
content-security-policy-report-only
script-src 'none'; form-action 'none'; frame-src 'none'; report-uri https://csp.withgoogle.com/csp/scaffolding/ascnsrsggc:122:0
report-to
{"group":"ascnsrsggc:122:0","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/scaffolding/ascnsrsggc:122:0"}],}
expires
Fri, 01 Jan 1990 00:00:00 GMT
access-control-allow-origin
https://www.revouninstaller.com
cross-origin-opener-policy-report-only
same-origin; report-to=ascnsrsggc:122:0
content-length
0
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 15 May 2025 10:03:12 GMT
content-type
text/plain
server
Golfe2
GET
H2
200
ga-audiences
www.google.pt/ads/
42 B
408 B
269ms
99ms
Image
image/gif
142.250.181.227
GOOGLE
General
Full URL
https://www.google.pt/ads/ga-audiences?v=1&t=sr&slf_rd=1&_r=4&tid=G-P73P80145H&cid=1371600675.1747303391&gtm=45je55d1v869118035z871855269za200zb71855269&aip=1&dma=1&dma_cps=syphamo&gcs=G111&gcd=13t3t3t2t5l1&npa=0&frm=0&tag_exp=101509157~103116026~103130498~103130500~103200004~103207802~103233427~103252644~103252646~103263073~103301114~103301116&ptag_exp=101509157~103116026~103130498~103130500~103200004~103233427~103252644~103252646~103301114~103301116&tag_exp=101509157~103116026~103130498~103130500~103200004~103207802~103233427~103252644~103252646~103263073~103301114~103301116&ptag_exp=101509157~103116026~103130498~103130500~103200004~103233427~103252644~103252646~103301114~103301116&z=419794290
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.250.181.227 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
fra16s56-in-f3.1e100.net
Software
cafe /
Resource Hash
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

cache-control
no-cache, no-store, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
42
date
Thu, 15 May 2025 10:03:13 GMT
x-xss-protection
0
content-type
image/gif
server
cafe
POST
H2
204
collect
region1.analytics.google.com/g/
0
0
72ms
71ms
Fetch
text/plain
216.239.34.36
GOOGLE
General
Full URL
https://region1.analytics.google.com/g/collect?v=2&tid=G-P73P80145H&gtm=45je55d1v869118035z871855269za200zb71855269&_p=1747303389200&gcs=G111&gcd=13t3t3t2t5l1&npa=0&dma_cps=syphamo&dma=1&tag_exp=101509157~103116026~103130498~103130500~103200004~103207802~103233427~103252644~103252646~103263073~103301114~103301116&ptag_exp=101509157~103116026~103130498~103130500~103200004~103233427~103252644~103252646~103301114~103301116&gdid=dNjAwYj&cid=1371600675.1747303391&ul=pt-pt&sr=1600x1200&uaa=&uab=&uafvl=&uamb=0&uam=&uap=&uapv=&uaw=0&are=1&pae=1&frm=0&pscdl=noapi&_eu=AAAAAAQ&_s=2&sid=1747303390&sct=1&seg=0&dl=https%3A%2F%2Fwww.revouninstaller.com%2Ffree-install-thankyou%2F&dt=Thank%20you%20for%20installing%20Revo%20Uninstaller%20Free&_tu=QA&en=page_load_time&epn.loading_time_sec=3.32&_et=4&tfd=9374
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtag/js?id=G-P73P80145H&cx=c&gtm=45He55d1v71855269za200&tag_exp=101509157~103116026~103130498~103130500~103200004~103233427~103252644~103252646~103301114~103301116
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
216.239.34.36 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
Software
Golfe2 /
Resource Hash

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/136.0.0.0 Safari/537.36
Referer
https://www.revouninstaller.com/

Response headers

cache-control
no-cache, no-store, must-revalidate
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
content-security-policy-report-only
script-src 'none'; form-action 'none'; frame-src 'none'; report-uri https://csp.withgoogle.com/csp/scaffolding/ascnsrsggc:153:0
report-to
{"group":"ascnsrsggc:153:0","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/scaffolding/ascnsrsggc:153:0"}],}
expires
Fri, 01 Jan 1990 00:00:00 GMT
access-control-allow-origin
https://www.revouninstaller.com
cross-origin-opener-policy-report-only
same-origin; report-to=ascnsrsggc:153:0
content-length
0
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 15 May 2025 10:03:17 GMT
content-type
text/plain
server
Golfe2

Verdicts & Comments Add Verdict or Comment

55 JavaScript Window variables

These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.

object| 0 object| 1 object| 2 object| 3 object| 4 object| dataLayer function| $ function| jQuery function| gtag string| src object| cf_s object| __COOKIE_BANNER_SETTINGS__ function| show function| hide function| iFrameResize object| zEWebpackACJsonp function| zE function| zEmbed object| lazySizesConfig object| chunkCB function| addCFGTMConsentListener number| __COOKIE_BANNER_INIT_TIME__ function| Popper object| bootstrap object| lazySizes function| setCookie function| getCookie function| labnolThumb function| labnolIframe object| Modernizr object| eapps object| Trustpilot object| google_tag_manager object| google_tag_data string| GoogleAnalyticsObject function| ga function| fbq function| _fbq function| twq function| onYouTubeIframeAPIReady object| googletag boolean| zEACLoaded object| regeneratorRuntime object| twttr object| gaplugins object| gaGlobal object| gaData boolean| CF_visiblity object| CookieFirst function| cookiefirst_show_settings object| webpackChunkformBuilder function| eappsFormBuilder object| formBuilder boolean| MotionIsMounted function| $zopim

17 Cookies

Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.

Domain/Path Expires Name / Value
www.revouninstaller.com/ 1969-12-31
23:59:59
Name: PHPSESSID
Value: op9m2cjn84sahs9schhvtjp4hn
www.revouninstaller.com/ 1970-01-21
14:07:19
Name: pll_language
Value: en
www.revouninstaller.com/ 1970-01-21
06:04:55
Name: show_popup
Value: 1
.revouninstaller.com/ 1970-01-21
07:31:19
Name: _gcl_au
Value: 1.1.315310286.1747303391
core.service.elfsight.com/ 1970-01-21
05:21:43
Name: elfsight_viewed_recently
Value: 1
.elfsight.com/ 1970-01-21
05:21:45
Name: __cf_bm
Value: l1asa0BniqJd6Xn5Jk4WUStT2tyik7sCsaMh0OC5ayU-1747303390-1.0.1.1-jPtP4jejv_N.fVbXxbVKDiRbH5XFtP0YLy0Ag5vcc.xntE1X6VHQf9U_PfMCNW7D.1Hl.Eilnt_nqvGIoxNgX1qEfaw1hhqu7e3PBqfkr_8
.revouninstaller.com/ 1970-01-21
05:23:09
Name: _gid
Value: GA1.2.1809515989.1747303391
.revouninstaller.com/ 1970-01-21
05:21:43
Name: _gat_UA-1917045-1
Value: 1
.t.co/ 1970-01-21
14:57:43
Name: muc_ads
Value: ac328553-e229-4b1e-8848-ac0da4688b0b
.t.co/ 1970-01-21
05:21:45
Name: __cf_bm
Value: SZy3I5Ia7fOzF3QDbtzzrqAOUaUZtTUMKXp2qYS9T4E-1747303391-1.0.1.1-oYK.ZMO7Z95rlpYKgAgBGICD0VG1.3Ybhz8oJEOgw8j6aBsFySBfvwYb1BnFwsm2OvLfSeN6OARefGYCttLKXpz3hq.VX6uCjvuqh8CtYuI
.twitter.com/ 1970-01-21
14:57:43
Name: personalization_id
Value: "v1_bdasQTVhQbFJknkvnlBcMw=="
.twitter.com/ 1970-01-21
05:21:45
Name: __cf_bm
Value: xMyGdFhDIml75zx26TuMC9nzfI4y40he0IT5ZghuHjU-1747303391-1.0.1.1-rkZHSTEN4P42n4RI0GCFDxNeRm5llHVi5p.qvu7Cfs1V8Kn2067TVwpfrQHgDRIh3Swt2o3zFb0tYZTBq01o2mOQ6k2E3n83VxyGzYO43qo
.revouninstaller.com/ 1970-01-21
07:31:19
Name: _fbp
Value: fb.1.1747303391377.567601859912204072
widget-mediator.zopim.com/ 1970-01-21
05:31:48
Name: AWSALBCORS
Value: RzJHjqrOYDafMyf3lvWJ2Yio0Rz/5RSUaTfuvrPsRWPACJ+CnplYIdPPyBNX4D9jca6P+0pJGIfuTeDSK14ZmG+H5FqonJHVrsS3qVvoHWpWYzV0kz55C+axGipO
.revouninstaller.com/ 1970-01-21
14:07:19
Name: __zlcmid
Value: 1RfncDzEUPK73ON
.revouninstaller.com/ 1970-01-21
14:57:43
Name: _ga
Value: GA1.1.1371600675.1747303391
.revouninstaller.com/ 1970-01-21
14:57:43
Name: _ga_P73P80145H
Value: GS2.1.s1747303390$o1$g0$t1747303391$j59$l0$h0

Security Headers

This page lists any security headers set by the main page. If you want to understand what these mean and how to use them, head on over to this page

Header Value
Content-Security-Policy frame-ancestors 'self';
Strict-Transport-Security max-age=31536000; includeSubdomains
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 1; mode=block

Indicators

This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.

ajax.googleapis.com
analytics.twitter.com
app.mailjet.com
cdn.jsdelivr.net
connect.facebook.net
consent.cookiefirst.com
core.service.elfsight.com
edge.cookiefirst.com
ekr.zdassets.com
f057a20f961f56a72089-b74530d2d26278124f446233f95622ef.ssl.cf1.rackcdn.com
fonts.googleapis.com
fonts.gstatic.com
region1.analytics.google.com
stackpath.bootstrapcdn.com
static.ads-twitter.com
static.elfsight.com
static.zdassets.com
stats.g.doubleclick.net
t.co
v2assets.zopim.io
vsrevogroup.zendesk.com
widget.trustpilot.com
www.facebook.com
www.google-analytics.com
www.google.com
www.google.pt
www.googletagmanager.com
www.revouninstaller.com
104.16.174.226
104.16.200.19
104.18.10.207
104.22.69.95
142.250.181.227
142.250.184.202
142.250.185.234
142.250.186.100
142.250.186.72
142.251.168.154
146.20.152.114
146.75.116.157
157.240.252.13
157.240.252.35
162.159.140.229
169.150.247.36
169.150.247.38
172.66.0.227
216.198.54.1
216.198.54.3
216.239.34.36
216.239.38.178
216.58.206.35
23.57.20.115
34.96.102.8
52.222.236.107
52.222.236.71
05069cc62b394b6ecc2daf3c51b4b2ba7f6cc8735988e8234487234af47eceee
07fb86f93b0017be8ade6eea3eac28f6178b2df898fe5f644996674a5a58ca78
0b8e6a0503148db0c445d26d7aef6a8de1d31b68a30f212ab47b6d4e7400f6bb
0c3217fe5cc4c6f1a2ea526e5e34167790df7661199b94e317ee720c8cec27ca
141e047935b2321d0c8a17e76f4a78eba0aadda8af0ef27fb5bd6b905ddb0b3d
1cffc2b3146584685cd72751d7f28aa030ab9ae2f1bc78f2c27909f8d8287b26
24d7b59ef3e2a233984a1ae5558b9ea09e58e616ce5c0c707f126781869aeaec
296f5722ef36477feb23f79b20a628df8baf4527d29e16ff161a5bc95dca3890
2ad82d5c83c9ec058a1efbb568c497093d249190abad9d51bcd42869683fddb1
2d1a1605140685d005db91fac1250f9d4b60566b565ab08740aa1c67ba4b104c
2f193d706417bcf72a130968908edcd09a192c51f4b592114ea4697ee4dfe85b
2ff5b959fa9f6b4b1d04d20a37d706e90039176ab1e2a202994d9580baeebfd6
330ee0ac92dec8a04ba432b9bf5d171330454e553cb46c18d96fdb925ee310dd
345a7f619e726c9ed21fa1e83646623f3491056eb1c9e0f3af797c42d38255c1
38fd706cbe82da3c705e708d889851bc1565dafc9a3d72d4c5527e7bcf13a933
3ad72d04b863fc860a2f724f27820ad7b2699614a91dcd4c0bdd06f57685ec75
3c4d6a1421c7ddb7e404521fe8c4cd5be5af446d7689cd880be26612eaad3cfa
3daa33db1794c557a0c63358f0ac20ffc31890f841c406df16d5894c1319a07e
402179b88fa6e0b17851d64725ec39658d804bd6cc9b8ba227e27bd3b4cca459
4148d0c90ebd46c31db6786edc9679893db53c97e68fee894309bdf9913cc9d5
4288b1e018ceffbce943fa7d4664ea4e8e9f1c0395ec549dc8166c7a3b206f87
4302eac6f74fb5f3ff2229402ddb0bef9a518f8188319428d157159768fa2366
4921a0babdab48814eee76ca2b58b5b1b7dfb90e801db7aaad98230acfd9eb37
4a43f37a56077705cd95fb9d3b20c5a660b3a2ffbab855f8730dcecb8432e496
501eff36e8442488336a3dd4d7532886979a6f2f062c4f094b519a78d508733f
52dc24c0429ea6ccc5b579a6da8bb79bf41e471fe5108a62009f3c2e195551c0
547dda3c14b284819be511be1e410da94a5efc6ccc4a9afe1c75394f9333191a
5486d67c53956813c2ab1fdef773516ee85aff7adae4ae0186cf09e398c1e28f
568849a9b53202c322377a9061b5f918fd01fffe5e76783afe5d323a1d6400a6
598f66a650667901cdce56b575211d5ab0fd5e0e164df032df0c63e9a12ebe42
5aa53525abc5c5200c70b3f6588388f86076cd699284c23cda64e92c372a1548
5c37189fb9387be170c36a9b799e1a6ce3f7f016a79b2c7032ed14be8597509c
6040808e83425cfbe1205aafa193cbf31e09ceae50f32f1709ae2e1472bac545
639d02df457ed5e83465da0306131f5a083f17395434c2f474b2adc413692bd9
63cacefe7f2da164f756fd92658d8285f28e44e245c1632b4f675131e751bbd6
6434052af0ddf6b0203fc314c95448d2148edc35dab8973128a46430fd6152c2
6625bc05fe0b30643675381684b69b0a7795863cac0cd88bc3967c9b23483ba2
688d6577ebeea79fd6e9ab9d09f9ac69a2cca4e6f2060776e9326aba482176bd
69294444ea55c3f1d0b1ef7524cbc7def9c8255f178518d511a195c94fd72c68
6bb1455c84f2e77d8fef44e02368071910a667b8edb24367c3f3ca9c4d2eca42
6c726f6d1377f7bc870d49c8f6c323e9a52e35caff10b8a54e04b565c471d60f
6e9fa14c90e4d77cb1490ba8c8437c87e8a624ebebb6c09ab8fb0b86fd50163d
70643c4dd06e40c19d5f6ed2d0a5d448394cd21ab9b1d9650060dede45535a8a
7a4e9eaad077165880b982842cc79f705c883e584c3fedaa1f2a97c016e697a3
7bdc4fd1b52f88617553782da88299fc8551f6921d5a30c5a29b96cb8b4c3eae
7ce23bb169d56e3dc218181172c5d318dc16526e035b539e038f605a893ea551
7dfe84faf51f33af5a66f356a57efcc53951f01c7529deb3e6edab005e72ae0d
7e510e61c497d334da21eccda06df5d3a428c9ea94d6903b6138e7c7255aba0f
898736a5f0d5891ededfcd9942475967c407a8f1243b28a6d3536ba98c44fbcb
89f154c58e6daffa0085f4d6ac74cbcdecbdd190fda50d34777265102458fb68
91e8f868eef6967dcfca5eeb8e428184a0f4dcd017246c78138e71e158a78db7
936cb6d96f115d51e7a2ac5aa09bb2c247a7daa04951ff4b82dd14518ff2e6af
941ce302a58a370422466e73e52f341477e5e10dbe976bb7dc4ef91821c28545
96e803cc46ba31cef48752356a13dc8a92564f2e6b20adcd4d360410b5fbc579
9bf6bf3dcc07223416fc8bbb8f49bff57d21c1c6dffd76f38f8c11e7d054c340
a7ae4f4e313e150000175511c29ca19ae2948eb663987253d19a9372cc20e3fe
aa7b6c81e85551eeb5c4809f1e683efa0b780c33d12ddfc2067a1b136803e45a
ac8778041fdb7f2e08ceb574c9a766247ea26f1a7d90fa854c4efcf4b361a957
ae5652f3e21d76b7d544f5fb02ab35c38799b897fd789675f110dbf1966e90a7
afabc7377364e0e73475342d61d6e519e833aa63806db5fc8043458c8fa711b5
b31c1f88534ee7c8830364c8c448069f88df370243dc6c55ca2f6cc97a1a717b
b3c5626f31221e5785725f4f4ff261565eb5f25b4377961ce9adc2616d20cfb3
b4855cc8ec721cbaf27f3c907345e101b1524858221c14faa79df34cb2f84991
b7d183dce188ef91df5ddcd9ff5378e1b64ce515ccb048ed2a1f32d4fd0a0a3e
b87b92cd9b2943bcc97a64011eb833ef4205009327eaffe17db1cd001ae9ecc8
bd25bde9fc4427cd6f3babcb8f888fe6174ca48881c103e243d4c6f83f30aab6
c0da39dfab2a366de1c0efa54c349ef46cdb40d083882d3fc7530de710845cf2
c4fada4accfa24704b54248bc5ce84acac50b6a059828b7714fe3006786c80c1
c69de41dda83f00cc1b13dba90a57f25df046286ecd227bdd0c4d51d94947b61
c7631939bbc2c74fc9a5fb1ee9565250a15bf95cc0e364da7fc5f15e3db41427
c776195ad46333c6c9a9fe3c74502ffea9a02faf122388ea3567922cc65a3060
c9db31d43b24c3f411603160fc6554ceb91e1c628696646a13a563feddee0540
cb6f2d32c49d1c2b25e9ffc9aaafa3f83075346c01bcd4ae6eb187392a4292cf
ce33194867312cfba76a4d9c6525a906ad8f3562b70a95e4175fc8a67b54e2d1
d077807b2373375b2d5c8ffbfeeea0bcb152e29c21ec147aecfab6b5502e5463
d120ab6f69b81ca09bbd82efab8e2e472d15e2233a7d765d3c7a1c2e1945dc95
d2614cd932db07243a69aee3ec8797c765f5210d4b38795b77cc60fd74d7c2cf
d36b373b44b77f016e4b7df913ba2da2a8025456f016bc794861f210c0e3ada3
d5bbdcb19982fe95732f1402bd8cadcf407746cec57fa18043f6dd7b3dbf2502
de36e50194320a7d3ef1ace9bd34a875a8bd458b253c061979dd628e9bf49afd
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
e69e78bce7fcba24d0b97671983c4ac0148d1cd9fb10e149d30be8b947c4eab4
e7902b56545718b3f9dcc015b4acab60270239d559b0adaae9e5c81dd95a89a1
e956a757317f4346a99bc7317d6accf3ffb49c89a3e6a031eb2218de4af224f8
eb2902ff32366de00d3afa351aeceb1357d5a468eacbb2fd92cf115276d626cb
ee43de7f6648dac36980de3bcf1bf0d34f07178fdb8afac80541f5cf1660cc5d
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
f2cbf1df88192121c656a71c19c615162f06366cd47947dc552550880e6094e4
f33c7bd75e8107b0e2c531d98af84d90780d913f9246e796ea633d948d91f709
f3d0577d1af48acc04dc362dbd48e435471ada60e3a1c9a60e129c22e719fd17
f7199759c3dad40cc08d883170d02d116a713e97bfdb9fc207d3fd50c1222506
f7f6a5894f1d19ddad6fa392b2ece2c5e578cbf7da4ea805b6885eb6985b6e3d
fa0ca55c4ef6b064ff606cebee35597e67c781e4186dd51344a6492c0d3ec672