
piast-tourist.pl
145.239.31.66
Public Scan
Open in
urlscan Pro
https://piast-tourist.pl/trips/saska_szwajcariae23e1f 8yr old
Submission: On May 28 via api (May 28th 2025, 6:45:59 am UTC) from PL — Scanned from PL Go Pro
Only in urlscan Pro
- Select different country locations for Private Scans.
- Use a global network of additional scanning locations and residential IPs for scanning.
- Interact with pages while you are scanning them.
- Download files from remote websites.
- Scan websites on the Tor Network.
Summary
TLS certificate: Issued by E5 on April 26th 2025. Valid for: 3mo.
This is the only time piast-tourist.pl was scanned on urlscan.io!
urlscan.io Verdict: No classification
Domain & IP information
| IP Address | AS Autonomous System | ||
|---|---|---|---|
| 44 | 145.239.31.66 145.239.31.66 | 16276 (OVH OVH SAS) (OVH OVH SAS) | |
| 2 | 216.58.206.42 216.58.206.42 | 15169 (GOOGLE) (GOOGLE) | |
| 6 | 104.17.24.14 104.17.24.14 | 13335 (CLOUDFLAR...) (CLOUDFLARENET) | |
| 4 | 216.58.212.136 216.58.212.136 | 15169 (GOOGLE) (GOOGLE) | |
| 4 | 104.21.27.152 104.21.27.152 | 13335 (CLOUDFLAR...) (CLOUDFLARENET) | |
| 1 | 151.101.66.217 151.101.66.217 | 54113 (FASTLY) (FASTLY) | |
| 1 | 13.32.27.116 13.32.27.116 | 16509 (AMAZON-02) (AMAZON-02) | |
| 1 | 18.66.102.11 18.66.102.11 | 16509 (AMAZON-02) (AMAZON-02) | |
| 2 | 142.250.186.164 142.250.186.164 | 15169 (GOOGLE) (GOOGLE) | |
| 1 | 142.250.74.195 142.250.74.195 | 15169 (GOOGLE) (GOOGLE) | |
| 11 | 142.250.186.74 142.250.186.74 | 15169 (GOOGLE) (GOOGLE) | |
| 1 | 13.33.187.74 13.33.187.74 | 16509 (AMAZON-02) (AMAZON-02) | |
| 1 | 3.89.174.178 3.89.174.178 | 14618 (AMAZON-AES) (AMAZON-AES) | |
| 1 | 216.239.34.36 216.239.34.36 | 15169 (GOOGLE) (GOOGLE) | |
| 80 | 15 |
ASN15169 (GOOGLE, US)
PTR: lhr35s10-in-f10.1e100.net
| fonts.googleapis.com 10yr old |
ASN15169 (GOOGLE, US)
PTR: fra16s46-in-f8.1e100.net
| www.googletagmanager.com 14yr old |
ASN16509 (AMAZON-02, US)
PTR: server-13-32-27-116.fra56.r.cloudfront.net
| cdn.heapanalytics.com 13yr old |
ASN16509 (AMAZON-02, US)
PTR: server-18-66-102-11.fra56.r.cloudfront.net
| static.hotjar.com 10yr old |
ASN15169 (GOOGLE, US)
PTR: fra24s08-in-f4.1e100.net
| www.google.com 14yr old |
ASN15169 (GOOGLE, US)
PTR: fra24s02-in-f3.1e100.net
| maps.gstatic.com 10yr old |
ASN15169 (GOOGLE, US)
PTR: fra24s05-in-f10.1e100.net
| maps.googleapis.com 10yr old |
ASN16509 (AMAZON-02, US)
PTR: server-13-33-187-74.fra60.r.cloudfront.net
| script.hotjar.com 10yr old |
ASN14618 (AMAZON-AES, US)
PTR: ec2-3-89-174-178.compute-1.amazonaws.com
| heapanalytics.com 14yr old |
| Apex Domain Subdomains |
Transfer | |
|---|---|---|
| 44 |
piast-tourist.pl
piast-tourist.pl 8yr old |
1 MB |
| 13 |
googleapis.com
fonts.googleapis.com — Cisco Umbrella Rank: 107 10yr old maps.googleapis.com — Cisco Umbrella Rank: 772 10yr old |
226 KB |
| 6 |
cloudflare.com
cdnjs.cloudflare.com — Cisco Umbrella Rank: 296 13yr old |
215 KB |
| 4 |
fontawesome.com
use.fontawesome.com — Cisco Umbrella Rank: 1446 10yr old |
89 KB |
| 4 |
googletagmanager.com
www.googletagmanager.com — Cisco Umbrella Rank: 100 14yr old |
398 KB |
| 2 |
google.com
www.google.com — Cisco Umbrella Rank: 9 14yr old |
1 KB |
| 2 |
hotjar.com
static.hotjar.com — Cisco Umbrella Rank: 1171 10yr old script.hotjar.com — Cisco Umbrella Rank: 1552 10yr old |
62 KB |
| 2 |
heapanalytics.com
cdn.heapanalytics.com — Cisco Umbrella Rank: 9005 13yr old heapanalytics.com — Cisco Umbrella Rank: 6293 14yr old |
38 KB |
| 1 |
google-analytics.com
region1.google-analytics.com — Cisco Umbrella Rank: 1949 5yr old |
|
| 1 |
gstatic.com
maps.gstatic.com 10yr old |
64 KB |
| 1 |
sentry-cdn.com
js.sentry-cdn.com — Cisco Umbrella Rank: 7519 8yr old |
2 KB |
| 80 | 11 |
| Domain | Requested by | |
|---|---|---|
| 44 | piast-tourist.pl |
piast-tourist.pl
|
| 11 | maps.googleapis.com |
www.google.com
maps.googleapis.com |
| 6 | cdnjs.cloudflare.com |
piast-tourist.pl
cdnjs.cloudflare.com |
| 4 | use.fontawesome.com |
piast-tourist.pl
use.fontawesome.com |
| 4 | www.googletagmanager.com |
piast-tourist.pl
www.googletagmanager.com |
| 2 | www.google.com |
piast-tourist.pl
www.googletagmanager.com |
| 2 | fonts.googleapis.com |
piast-tourist.pl
|
| 1 | region1.google-analytics.com |
www.googletagmanager.com
|
| 1 | heapanalytics.com |
piast-tourist.pl
|
| 1 | script.hotjar.com |
static.hotjar.com
|
| 1 | maps.gstatic.com |
www.google.com
|
| 1 | static.hotjar.com |
piast-tourist.pl
|
| 1 | cdn.heapanalytics.com |
piast-tourist.pl
|
| 1 | js.sentry-cdn.com |
piast-tourist.pl
|
| 80 | 14 |
This site contains links to these domains. Also see Links.
| Domain |
|---|
| www.duo.com.pl |
| sklep.signal-iduna.pl |
| wszystkoociasteczkach.pl |
| www.facebook.com |
| www.instagram.com |
| vakanza.pl |
| Subject Issuer | Validity | Valid | |
|---|---|---|---|
| piast-tourist.pl E5 |
2025-04-26 - 2025-07-25 |
3mo | crt.sh |
| upload.video.google.com WE2 |
2025-05-12 - 2025-08-04 |
3mo | crt.sh |
| cdnjs.cloudflare.com WE1 |
2025-05-22 - 2025-08-20 |
3mo | crt.sh |
| *.google-analytics.com WE2 |
2025-05-12 - 2025-08-04 |
3mo | crt.sh |
| use.fontawesome.com WE1 |
2025-05-04 - 2025-08-02 |
3mo | crt.sh |
| *.sentry-cdn.com GlobalSign Atlas R3 DV TLS CA 2025 Q1 |
2025-04-07 - 2026-05-09 |
1yr | crt.sh |
| cdn.heapanalytics.com Amazon RSA 2048 M04 |
2025-04-28 - 2026-05-27 |
1yr | crt.sh |
| *.hotjar.com Amazon RSA 2048 M02 |
2025-04-22 - 2026-05-22 |
1yr | crt.sh |
| *.google.com WE2 |
2025-05-12 - 2025-08-04 |
3mo | crt.sh |
| *.gstatic.com WE2 |
2025-05-12 - 2025-08-04 |
3mo | crt.sh |
| heapanalytics.com Amazon RSA 2048 M03 |
2024-11-18 - 2025-12-17 |
1yr | crt.sh |
This page contains 3 frames:
Primary Page:
https://piast-tourist.pl/trips/saska_szwajcariae23e1f
Frame ID: C58BEA7BE279947E16F92DF46CD4EA7A
Requests: 66 HTTP requests in this frame
Frame:
https://www.google.com/maps/embed?pb=!1m18!1m12!1m3!1d1256.4714339008954!2d14.07355732613042!3d50.96176054486222!2m3!1f0!2f0!3f0!3m2!1i1024!2i768!4f13.1!3m3!1m2!1s0x4709bad6f1ef2ee7%3A0x1d39e434742c2d6c!2sBastei!5e0!3m2!1spl!2spl!4v1649402918723!5m2!1spl!2spl
Frame ID: C2C5118A1D88F79E04F65E0973D1927D
Requests: 14 HTTP requests in this frame
Frame:
https://www.googletagmanager.com/static/service_worker/55j0/sw_iframe.html?origin=https%3A%2F%2Fpiast-tourist.pl
Frame ID: F51BFF9EFE474CE151CF658324F7162C
Requests: 1 HTTP requests in this frame
Screenshot
Go Pro
Only in urlscan Pro
Use the Visual Search feature to find pages with visually similar screenshots.
Click for more information
Free trials of urlscan Pro are available.
Page Title
Saska Szwajcaria - Piast TouristDetected technologies
 Google Maps
(Maps)
Expand
Detected patterns
- //maps\.google(?:apis)?\.com/maps/api/js
 Font Awesome
(Font scripts)
Expand
Detected patterns
- <link[^>]* href=[^>]*?(?:F|f)o(?:n|r)t-?(?:A|a)wesome(?:[^>]*?([0-9a-fA-F]{7,40}|[\d]+(?:.[\d]+(?:.[\d]+)?)?)|)
- (?:F|f)o(?:n|r)t-?(?:A|a)wesome(?:.*?([0-9a-fA-F]{7,40}|[\d]+(?:.[\d]+(?:.[\d]+)?)?)|)
 Google Analytics
(Analytics)
Expand
Detected patterns
 Google Font API
(Font scripts)
Expand
Detected patterns
- <link[^>]* href=[^>]+fonts\.(?:googleapis|google)\.com
 Google Tag Manager
(Tag managers)
Expand
Detected patterns
- googletagmanager\.com/gtag/js
 Heap
(Analytics)
Expand
Detected patterns
- heap-\d+\.js
 Hotjar
(Analytics)
Expand
Detected patterns
- //static\.hotjar\.com/
 jQuery
(JavaScript libraries)
Expand
Detected patterns
- /([\d.]+)/jquery(?:\.min)?\.js
- jquery.*\.js(?:\?ver(?:sion)?=([\d.]+))?
Page Statistics
6 Outgoing links
Go Pro
Only in urlscan Pro
Effortlessly use any on-page link as a pivot to discover other pages pointing to the exact same destination. Seamlessly trace both specific URLs and broader domains to uncover hidden connection networks and map out backlink relationships with ease.
Click for more information
Free trials of urlscan Pro are available.
These are links going to different origins than the main page.
Title: Wczasy lotnicze
Search URL Search Domain Scan URL
Title: Ubezpieczenie
Search URL Search Domain Scan URL
Title: Więcej
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Title: Vakanza
Search URL Search Domain Scan URL
Redirected requests
There were HTTP redirect chains for the following requests:
80 HTTP transactions
Go Pro
Only in urlscan Pro
Inspect WebSocket connections, examine POST data effortlessly, and track overlap counts in real time. Features live search and filtering across all HTTP output, complete with full response metadata for deep analysis.
Click for more information
Free trials of urlscan Pro are available.
1 data transactions
| Method Protocol |
Status | Resource Path |
Size x-fer |
Time Latency |
Type MIME-Type |
IP Location |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
|
GET H/1.1 |
200 OK |
Primary Request
saska_szwajcariae23e1f
Show response
piast-tourist.pl/trips/ |
169 KB 38 KB |
287ms
200ms |
Document
text/html |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
css2
fonts.googleapis.com/ |
28 KB 2 KB |
196ms
73ms |
Stylesheet
text/css |
216.58.206.42 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
css2
fonts.googleapis.com/ |
7 KB 736 B |
197ms
74ms |
Stylesheet
text/css |
216.58.206.42 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
fontawesome.min.css
cdnjs.cloudflare.com/ajax/libs/font-awesome/5.15.4/css/ |
57 KB 11 KB |
99ms
68ms |
Stylesheet
text/css |
104.17.24.14 CLOUDFLARENET |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
all.min.css
cdnjs.cloudflare.com/ajax/libs/font-awesome/5.15.4/css/ |
58 KB 11 KB |
71ms
40ms |
Stylesheet
text/css |
104.17.24.14 CLOUDFLARENET |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
trip_view.css
piast-tourist.pl/assets/css/user/ |
5 KB 1 KB |
60ms
33ms |
Stylesheet
text/css |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
reserve_trip_modal.css
piast-tourist.pl/assets/css/modals/ |
12 KB 2 KB |
116ms
56ms |
Stylesheet
text/css |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
fotorama.css
piast-tourist.pl/assets/css/vendors/ |
15 KB 3 KB |
116ms
56ms |
Stylesheet
text/css |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
user.css
piast-tourist.pl/assets/css/ |
913 KB 109 KB |
129ms
69ms |
Stylesheet
text/css |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
js
Show response
www.googletagmanager.com/gtag/ |
424 KB 140 KB |
238ms
140ms |
Script
application/javascript |
216.58.212.136 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
js
Show response
www.googletagmanager.com/gtag/ |
332 KB 115 KB |
193ms
95ms |
Script
application/javascript |
216.58.212.136 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
pl.png
piast-tourist.pl/assets/res/country_flags/ |
134 B 369 B |
90ms
28ms |
Image
image/png |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
en.png
piast-tourist.pl/assets/res/country_flags/ |
349 B 585 B |
198ms
114ms |
Image
image/png |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
fBN2mFrJHu8GsLD2KXcdkM5Ii9FoR2K6KRMUJKaB.jpg
piast-tourist.pl/storage/trip_images/700/ |
100 KB 101 KB |
87ms
75ms |
Image
image/jpeg |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
9qDeBVdZvg2jCOim5fcRRnDfvy1MPOVtrnzjxVT6.png
piast-tourist.pl/storage/trip_images/700/ |
173 KB 174 KB |
98ms
98ms |
Image
image/png |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
vVbvEcNuyChVzJf1XuL45xtTTXxrOo4s9l6IFXjL.jpg
piast-tourist.pl/storage/trip_images/700/ |
79 KB 80 KB |
71ms
71ms |
Image
image/jpeg |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
KOcRWdPBNvDvNFr0f9HASvqot2tsMjFEXor3V46T.jpg
piast-tourist.pl/storage/trip_images/700/ |
111 KB 113 KB |
77ms
77ms |
Image
image/jpeg |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
7MC1kapaU597SYY8Hs9hrpXHo1FKg71eTXlX41QP.jpg
piast-tourist.pl/storage/trip_images/700/ |
118 KB 119 KB |
93ms
92ms |
Image
image/jpeg |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
jquery.min.js
Show response
cdnjs.cloudflare.com/ajax/libs/jquery/3.4.1/ |
86 KB 28 KB |
41ms
41ms |
Script
application/javascript |
104.17.24.14 CLOUDFLARENET |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
app.js
Show response
piast-tourist.pl/assets/js/ |
1 MB 327 KB |
48ms
47ms |
Script
application/javascript |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
jquery.selectric.min.js
Show response
piast-tourist.pl/assets/js/vendors/ |
14 KB 5 KB |
55ms
55ms |
Script
application/javascript |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
jquery.mask.js
Show response
piast-tourist.pl/assets/js/vendors/ |
23 KB 6 KB |
58ms
56ms |
Script
application/javascript |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
jquery.cookie.js
Show response
piast-tourist.pl/assets/js/vendors/ |
3 KB 2 KB |
32ms
29ms |
Script
application/javascript |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
send_technical_message_modal.js
Show response
piast-tourist.pl/assets/js/modals/ |
487 B 512 B |
32ms
29ms |
Script
application/javascript |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
notifications_modal.js
Show response
piast-tourist.pl/assets/js/modals/ |
1 KB 758 B |
35ms
31ms |
Script
application/javascript |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
b219f80601.js
Show response
use.fontawesome.com/ |
9 KB 4 KB |
121ms
36ms |
Script
text/javascript |
104.21.27.152 CLOUDFLARENET |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
3fd13d52b717475bb4a4176259ced50c.min.js
Show response
js.sentry-cdn.com/ |
3 KB 2 KB |
202ms
85ms |
Script
text/javascript |
151.101.66.217 FASTLY |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
trip_view.js
Show response
piast-tourist.pl/assets/js/user/ |
186 B 441 B |
31ms
31ms |
Script
application/javascript |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
fotorama.js
Show response
piast-tourist.pl/assets/js/vendors/ |
40 KB 17 KB |
41ms
41ms |
Script
application/javascript |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
logo-blik.svg
piast-tourist.pl/assets/res/payments/ |
5 KB 5 KB |
30ms
30ms |
Image
image/svg+xml |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
PKO.png
piast-tourist.pl/assets/res/payments/ |
10 KB 10 KB |
34ms
34ms |
Image
image/png |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
pekao.png
piast-tourist.pl/assets/res/payments/ |
8 KB 8 KB |
31ms
31ms |
Image
image/png |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
santander.png
piast-tourist.pl/assets/res/payments/ |
5 KB 5 KB |
73ms
73ms |
Image
image/png |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
ING.png
piast-tourist.pl/assets/res/payments/ |
9 KB 9 KB |
49ms
49ms |
Image
image/png |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
BNP_Paribas.png
piast-tourist.pl/assets/res/payments/ |
7 KB 7 KB |
61ms
60ms |
Image
image/png |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
mBank.png
piast-tourist.pl/assets/res/payments/ |
4 KB 4 KB |
56ms
56ms |
Image
image/png |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
Millenium.png
piast-tourist.pl/assets/res/payments/ |
4 KB 5 KB |
30ms
30ms |
Image
image/png |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
alior.png
piast-tourist.pl/assets/res/payments/ |
17 KB 17 KB |
57ms
56ms |
Image
image/png |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
Credit_Agricole.png
piast-tourist.pl/assets/res/payments/ |
7 KB 7 KB |
54ms
54ms |
Image
image/png |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
bank_pocztowy.png
piast-tourist.pl/assets/res/payments/ |
5 KB 5 KB |
31ms
31ms |
Image
image/png |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
BOS.png
piast-tourist.pl/assets/res/payments/ |
10 KB 10 KB |
39ms
39ms |
Image
image/png |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
Inteligo.png
piast-tourist.pl/assets/res/payments/ |
5 KB 5 KB |
31ms
31ms |
Image
image/png |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
logo-tpay.svg
piast-tourist.pl/assets/res/payments/ |
20 KB 21 KB |
30ms
30ms |
Image
image/svg+xml |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
reserve_trip_modal.js
Show response
piast-tourist.pl/assets/js/modals/ |
48 KB 11 KB |
56ms
56ms |
Script
application/javascript |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
reserve_list_trip_modal.css
piast-tourist.pl/assets/css/modals/ |
2 KB 954 B |
38ms
38ms |
Stylesheet
text/css |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
reserve_list_trip_modal.js
Show response
piast-tourist.pl/assets/js/modals/ |
2 KB 875 B |
29ms
29ms |
Script
application/javascript |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
preliminary_list_trip_modal.css
piast-tourist.pl/assets/css/modals/ |
2 KB 992 B |
30ms
29ms |
Stylesheet
text/css |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
preliminary_list_trip_modal.js
Show response
piast-tourist.pl/assets/js/modals/ |
3 KB 1 KB |
29ms
29ms |
Script
application/javascript |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
heap-4190459831.js
Show response
cdn.heapanalytics.com/js/ |
119 KB 38 KB |
221ms
87ms |
Script
application/javascript |
13.32.27.116 AMAZON-02 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
hotjar-3159621.js
Show response
static.hotjar.com/c/ |
15 KB 6 KB |
252ms
104ms |
Script
application/javascript |
18.66.102.11 AMAZON-02 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
logo_medium.png
piast-tourist.pl/storage/page_images/logos/color/ |
76 KB 78 KB |
79ms
67ms |
Image
image/png |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
fa-regular-400.woff2
cdnjs.cloudflare.com/ajax/libs/font-awesome/5.15.4/webfonts/ |
13 KB 14 KB |
36ms
35ms |
Font
application/octet-stream |
104.17.24.14 CLOUDFLARENET |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
fa-solid-900.woff2
cdnjs.cloudflare.com/ajax/libs/font-awesome/5.15.4/webfonts/ |
76 KB 77 KB |
88ms
88ms |
Font
application/octet-stream |
104.17.24.14 CLOUDFLARENET |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
fa-brands-400.woff2
cdnjs.cloudflare.com/ajax/libs/font-awesome/5.15.4/webfonts/ |
75 KB 76 KB |
37ms
36ms |
Font
application/octet-stream |
104.17.24.14 CLOUDFLARENET |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
embed
Show response
www.google.com/maps/ Frame C2C5 |
2 KB 1 KB |
240ms
182ms |
Document
text/html |
142.250.186.164 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
b219f80601.css
use.fontawesome.com/ |
1 KB 840 B |
39ms
38ms |
Stylesheet
text/css |
104.21.27.152 CLOUDFLARENET |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
fotorama.png
piast-tourist.pl/assets/css/vendors/ |
3 KB 3 KB |
42ms
29ms |
Image
image/png |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
flags.webp
piast-tourist.pl/assets/img/ |
28 KB 28 KB |
45ms
38ms |
Image
image/webp |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
font-awesome-css.min.css
use.fontawesome.com/releases/v4.7.0/css/ |
30 KB 7 KB |
36ms
36ms |
Stylesheet
text/css |
104.21.27.152 CLOUDFLARENET |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
init_embed.js
Show response
maps.gstatic.com/maps-api-v3/embed/js/61/1/intl/pl_ALL/ Frame C2C5 |
240 KB 64 KB |
289ms
69ms |
Script
text/javascript |
142.250.74.195 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
js
Show response
maps.googleapis.com/maps/api/ Frame C2C5 |
12 KB 3 KB |
314ms
94ms |
Script
text/javascript |
142.250.186.74 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
modules.f5772d147096c4644991.js
Show response
script.hotjar.com/ |
224 KB 56 KB |
278ms
82ms |
Script
application/javascript |
13.33.187.74 AMAZON-02 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
h
heapanalytics.com/ |
37 B 378 B |
615ms
312ms |
Image
image/gif |
3.89.174.178 AMAZON-AES |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
200 |
collect
www.google.com/ccm/ |
0 0 |
116ms
57ms |
Fetch
text/plain |
142.250.186.164 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
js
Show response
www.googletagmanager.com/gtag/ |
424 KB 140 KB |
79ms
79ms |
Script
application/javascript |
216.58.212.136 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
sw_iframe.html
Show response
www.googletagmanager.com/static/service_worker/55j0/ Frame F51B |
3 KB 2 KB |
181ms
61ms |
Document
text/html |
216.58.212.136 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
fontawesome-webfont.woff2
use.fontawesome.com/releases/v4.7.0/fonts/ |
75 KB 76 KB |
120ms
37ms |
Font
application/font-woff2 |
104.21.27.152 CLOUDFLARENET |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
collect
region1.google-analytics.com/g/ |
0 0 |
154ms
53ms |
Fetch
text/plain |
216.239.34.36 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
search.js
Show response
maps.googleapis.com/maps-api-v3/api/js/61/1/intl/pl_ALL/ Frame C2C5 |
3 KB 2 KB |
75ms
73ms |
Script
text/javascript |
142.250.186.74 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
geometry.js
Show response
maps.googleapis.com/maps-api-v3/api/js/61/1/intl/pl_ALL/ Frame C2C5 |
3 KB 1 KB |
107ms
107ms |
Script
text/javascript |
142.250.186.74 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
main.js
Show response
maps.googleapis.com/maps-api-v3/api/js/61/1/intl/pl_ALL/ Frame C2C5 |
242 KB 70 KB |
76ms
75ms |
Script
text/javascript |
142.250.186.74 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
gen_204
Show response
maps.googleapis.com/maps/api/mapsjs/ Frame C2C5 |
3 B 45 B |
70ms
69ms |
XHR
application/json |
142.250.186.74 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
common.js
Show response
maps.googleapis.com/maps-api-v3/api/js/61/1/intl/pl_ALL/ Frame C2C5 |
122 KB 36 KB |
60ms
60ms |
Script
text/javascript |
142.250.186.74 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
util.js
Show response
maps.googleapis.com/maps-api-v3/api/js/61/1/intl/pl_ALL/ Frame C2C5 |
321 KB 73 KB |
51ms
51ms |
Script
text/javascript |
142.250.186.74 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
map.js
Show response
maps.googleapis.com/maps-api-v3/api/js/61/1/intl/pl_ALL/ Frame C2C5 |
82 KB 26 KB |
78ms
78ms |
Script
text/javascript |
142.250.186.74 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
overlay.js
Show response
maps.googleapis.com/maps-api-v3/api/js/61/1/intl/pl_ALL/ Frame C2C5 |
3 KB 1 KB |
114ms
114ms |
Script
text/javascript |
142.250.186.74 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET DATA |
200 OK |
truncated
/ Frame C2C5 |
6 KB 0 |
Image
image/svg+xml |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
onion.js
Show response
maps.googleapis.com/maps-api-v3/api/js/61/1/intl/pl_ALL/ Frame C2C5 |
31 KB 10 KB |
116ms
116ms |
Script
text/javascript |
142.250.186.74 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
search_impl.js
Show response
maps.googleapis.com/maps-api-v3/api/js/61/1/intl/pl_ALL/ Frame C2C5 |
3 KB 1 KB |
112ms
112ms |
Script
text/javascript |
142.250.186.74 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
4183.js
Show response
piast-tourist.pl/assets/js/ |
255 KB 58 KB |
54ms
54ms |
Script
application/javascript |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
32x32.png
piast-tourist.pl/storage/page_images/favicons/ |
1 KB 2 KB |
66ms
66ms |
Other
image/png |
145.239.31.66 OVH OVH SAS |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||










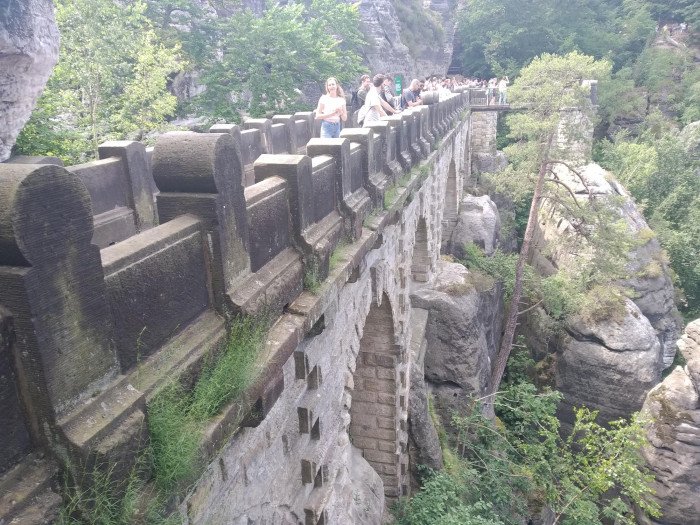







Verdicts & Comments Add Verdict or Comment
55 JavaScript Window variables
Go Pro
Only in urlscan Pro
Inspect and pivot on JavaScript variables, identifiers, and other key site metadata data with urlscan Pro. Reveal and search on client-side frameworks, runtime variables, and custom values.
Click for more information
Free trials of urlscan Pro are available.
These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.
object| 0 object| 1 object| 2 function| gtag object| dataLayer object| heap function| hj object| _hjSettings object| Laravel function| $ function| jQuery function| getCookie object| webpackChunk object| __SENTRY__ function| _ object| iziToast object| simpleslider function| Tokenfield function| tabs function| Color function| Chart function| croppie function| Quill function| ImageUploader object| imageUploader function| flatpickr function| rangePlugin function| monthSelectPlugin object| imguploader object| f object| panel object| front function| moment function| phoneInput object| app object| send_technical_message_modal object| notifications_modal object| FontAwesomeCdnConfig string| cssUrl object| Sentry object| ts object| tripView string| fotoramaVersion object| reserve_trip_modal object| reserve_list_trip_modal object| preliminary_list_trip_modal object| hjSiteSettings object| hjLazyModules function| hjBootstrap object| hjBootstrapCalled object| _sentryDebugIds object| google_tag_manager object| google_tag_data function| onYouTubeIframeAPIReady object| gaGlobal9 Cookies
Go Pro
Only in urlscan Pro
Review, search, and pivot on browser cookies and persistence site data to see how a site tracks users and keeps sessions alive across visits.
Click for more information
Free trials of urlscan Pro are available.
Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.
| Domain/Path | Expires | Name / Value | |||
|---|---|---|---|---|---|
| .piast-tourist.pl/ | 1970-01-21 15:08:12 |
Name: _hp2_id.4190459831 Value: %7B%22userId%22%3A%225968014167518273%22%2C%22pageviewId%22%3A%224026451995132940%22%2C%22sessionId%22%3A%227630505881976814%22%2C%22identity%22%3Anull%2C%22trackerVersion%22%3A%224.0%22%7D |
|||
| .piast-tourist.pl/ | 1970-01-21 07:49:50 |
Name: _gcl_au Value: 1.1.291894753.1748414760 |
|||
| .piast-tourist.pl/ | 1970-01-21 15:16:14 |
Name: _ga_WJ74R8G972 Value: GS2.1.s1748414760$o1$g0$t1748414760$j60$l0$h0 |
|||
| .piast-tourist.pl/ | 1970-01-21 15:16:14 |
Name: _ga Value: GA1.1.1379665571.1748414760 |
|||
| .piast-tourist.pl/ | 1970-01-21 14:25:50 |
Name: _hjSessionUser_3159621 Value: eyJpZCI6IjcwMzM0M2YxLWE3NTgtNTk0Yy1hZWQ1LTM0N2MzODk4ZmU0NyIsImNyZWF0ZWQiOjE3NDg0MTQ3NjAzMDMsImV4aXN0aW5nIjpmYWxzZX0= |
|||
| .piast-tourist.pl/ | 1970-01-21 05:40:16 |
Name: _hjSession_3159621 Value: eyJpZCI6IjUwZWM3YjJiLTE5NjktNGU1MS1iMGRhLTM3YmVlOTlmM2JkOSIsImMiOjE3NDg0MTQ3NjAzMDMsInMiOjAsInIiOjAsInNiIjowLCJzciI6MCwic2UiOjAsImZzIjoxLCJzcCI6MH0= |
|||
| .piast-tourist.pl/ | 1970-01-21 05:40:16 |
Name: _hp2_ses_props.4190459831 Value: %7B%22ts%22%3A1748414759968%2C%22d%22%3A%22piast-tourist.pl%22%2C%22h%22%3A%22%2Ftrips%2Fsaska_szwajcariae23e1f%22%7D |
|||
| piast-tourist.pl/ | 1970-01-21 14:25:50 |
Name: XSRF-TOKEN Value: eyJpdiI6IlV2Q3JZcFA0aElraDk1WUpSZHJrZmc9PSIsInZhbHVlIjoidFRYd0ZIM0xnUDR0RktVTHUyZHpZUTJmU20zWDBXQTlpVTdaeDYreHpPSjMwbmczaUZLbWgrK0UzSW1HNkxTNU90S0RsSWFZRTNPTk5uTUFXeGxKL0xtdnZ2Mmc0Q2tMSC9OU0NEeWpnRUlxNUVtSmlucFpEUzBpY1JHaVBhK1oiLCJtYWMiOiI5NjlhMTEzNWVhMTdmY2YxMGQ1ZDk5YmI2YzE5ZmQxMjdkNGNlNWZiYTlmM2ZiZDQ4MzM5NWQ0YzRmMWZhNjdlIiwidGFnIjoiIn0%3D |
|||
| piast-tourist.pl/ | 1970-01-21 14:25:50 |
Name: vakanza_session Value: eyJpdiI6ImxlUHlXYzJaampBOGpwTTUvSlE1Wnc9PSIsInZhbHVlIjoiWjVZNmZpNzFYVmNQSTVlRUVJUC81cC9hY3o4LzIyRW1rTEhwMTlIVHlPbzIwK08wRFZYcVlOMEMrZnpiRHJwYmIrUDRCMklhT3JOaVJlVmtRcTJaRzdzZlJSWkI0T0ttd3BhSm9CUTk5NTlRWlZocFp5SkQySmF4WFV2cVhxYlMiLCJtYWMiOiIxYjNkOWMxOTFiZTQ3ZDZiZTg1ZWYyZWE2N2U5YzRkMTlhMjY5ZjhhNzc2Y2Q1NWVlMGY0YzM5YzNmMWI3YTQ1IiwidGFnIjoiIn0%3D |
Indicators
This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.
cdn.heapanalytics.com
cdnjs.cloudflare.com
fonts.googleapis.com
heapanalytics.com
js.sentry-cdn.com
maps.googleapis.com
maps.gstatic.com
piast-tourist.pl
region1.google-analytics.com
script.hotjar.com
static.hotjar.com
use.fontawesome.com
www.google.com
www.googletagmanager.com
104.17.24.14
104.21.27.152
13.32.27.116
13.33.187.74
142.250.186.164
142.250.186.74
142.250.74.195
145.239.31.66
151.101.66.217
18.66.102.11
216.239.34.36
216.58.206.42
216.58.212.136
3.89.174.178
002dc6620b526f6196ca69d859d30f9a36f36d324c7278141bb924f2a6459719
01a3528eeb6b8866df2dadd7695cbc6a1d9fcd9ffa8ffc00c8a982c56dd0a8dc
0558983c6cae97bb749012fcf8339f61429d0fd0bb73f04ea2069d80fc2e4520
0588d1661498d804543dc1537f9784877a962b9f0ef3c4ccee765eb7f2543611
07bfe1d315831a538548340ac0aaa833f54bc23d6433ce688ff30a5aa2379a04
0925e8ad7bd971391a8b1e98be8e87a6971919eb5b60c196485941c3c1df089a
0e2a53ec4d77d08efa8e8f5fc86b1c25e8f2af39d6b44334e1219ed3e0687a61
0f44882c838799c3ce42679d9d589ab7dec7ffcb892dc2a8abf4b2da9a67212c
132ff8b5882d0bf199f16e7dc311272d177935c188b12ff9a661eb4505f5e074
144ca17f6d79d2d7ae8c63f83bc7d6d54c0a96876a22c20f497bf0beed551a61
1925258a2897f52a4b94afc3c581d1afd320b6e889bbb9f4688bb1440e2a69a1
1b23fb5fd4df14482a0992d3fe25d4392d04a1376fa98c4601f6581fb7780b78
1febfda26f41caacae574717ad736afb290ecd0b9f689a6d2fe2b9bf5749d20c
28321f3084e11838cdd055645cdd1bc34f34609d62d59c668b6391d912d61407
2adefcbc041e7d18fcf2d417879dc5a09997aa64d675b7a3c4b6ce33da13f3fe
33644ae75ae6475699206914c84e66ae63cff41967e3360b3b5d3cdd820564b9
381039a687e17cbec2406c2c86ed91fd467ccc1490e67a105d41103e30e32993
38cb2c18d031de178dac65b8e3e3783404501d21551fbdd02cfaf3f620e69790
3a1d4ffb2386305a1018e2f7adbea9598857bbec92f1a4d64230937238f0c6fb
4636ab1805332173a3407967cec32ff6eff4b40b9268d499df367697ea274e6c
4bffe5a663c7766cc056927879b45c6fa4f0f4967c0ff1c9fa528f2de2aa7e64
5b9573e1023da775390e9284ec0eb1c606df9b468a28980055b4a6aa804f4350
65c4065eaadd12a9742fb13820ec3d042747bf3b2a97f43dbf636a8eb9d51d58
692b84a9b543ac72088f0606454eb2a20809d7c454ac56feed3b651772a0ed95
6beb930a277160c9dea41aba58e3c7ebebcc68d1a3a20894ebce2f79db1a3555
6ed59e7c16215c2b205a187f18a4b637ede30ac2ed0322fc10283ceff2e0ae8d
6f843f1e6b1d0d97d8fc3fd72458bb0d4b0409a29b6d88f44d3aaeccf5f7aaed
729c9f5f52a80bbca4179636c859c1d66d9d35b494d3ab9cecaeee0cbcbc61af
73e3a1f3c7ec98f7e80dad38077ad9d5621ea7d8421755b1de408fd432c0e270
776f1cfeab4100a7bde30867e63ba00dbde27e1ed914339ba957fced67d5a290
78201116be4faaafc9eca0b176aea9f35e57479b8833ea857d3b06f4f0f0d2e8
782fb18a49158eb2c53b5e0708287f942687b325ea83faf942d2d885fb2a5c54
787410e41e7a953600a4c7969e727fefde6735a894404e2451aa9a5eaa33ba97
7fa660adfeb9e1699c3db67f3e85e7a5d6b92328465269362b2116bbb0f343e3
831636d4f3662b4f3571063605c143f88f0b313d17386d9d49359a533babfd2f
86792a12ea62bb35df26139ea1a96b1c98f881daaa69eb8867d52be572d04b53
8c478fb9c5f0c7065f37118c6e17a2ddaa60390a781a5482893fde5c4b92c985
8ea8791754915a898a3100e63e32978a6d1763be6df8e73a39d3a90d691cdeef
8ffc6f3f6211784c476b2cd37531a9eff91adfe6234da4787ad37191812b8511
919c8640240a9f480c6e4f7bc0f7cc768052bb8e4873588226e95ad3523d972e
96fe5f8f1456f8bbba13418966ba11224174272df48fd13f63dbc7e5f91463bd
9834b82ad26e2a37583d22676a12dd2eb0fe7c80356a2114d0db1aa8b3899537
99464ceb71bc9bbdcc72275faefe44f98eb5cbb6b5d8ee665b87b35376f1a96e
9c86b5a87331410b75efb1fad571a4fa45bf5a1db20993dd0da66a9a4432d8b4
a48be50060080a6e202990d6c03e58281353cccb0ed61b53a7202ce165a69f13
a8bbd534281ebff8c9b3c56cad5573262054089a1ddbb3d1c2febfb4122acf47
a8d11a7a518cc7cef35aaa5880bcb437d2ba15a6f5cc1184d530050d510581fa
aae64027f86a6bef4e1cf780739ac40263e4c4b31155c00e2feff9888d5d542e
abf6880e73714e8087b6e38a499766b013919422960c584d8b1ce912e8b6add5
b0044d91b724bb429337d6dcd9d2332e855bc0b4452c1d3fc9beea9973017521
b84161c9fbf7520cd14e7019f92120bd87a928a074156e91a992eba9fc9436e8
b88eca2ebe248d90e998efe7ed36fa92d45bef5bf181568b5bb1746db40b2347
b9aef84afa80b51758ab12e1ab8dea272379021c938e88719cb2c8e19a2c2713
bab8c120533653286d13397b360e3454272555da95eac2862c1ea6b59d7392c8
bb229a48bee31f5d54ca12dc9bd960c63a671f0d4be86a054c1d324a44499d96
bb42d8ca784a2904be105ea31645c2b58f0388154f7c6e49a066857d45e846a9
bbc254bf5c6a315535ee0fcce5a4f2da84ecdb9a3e3db9dd39317e3e7b114325
c27b07bac7d862ffafbf24b2a4b248ff9ce0ed00fdb5b81a5b434d465a237dd6
c5992da782c54136d0a7406cf141731f955abd2e397d1be72249e22922fbdd41
c5b62e8b995bf33780c41acd3c966792d48a40717f7f06189ddc3344a85e3574
c84e4b2e9e47490ff3fa125e0aa933f617633649358da8861b4b430ab6ae9a70
c88cba8eccaebad6a1b07c51c762f7c58bc92955ca44e21772b00590c41c6c48
ca3d163bab055381827226140568f3bef7eaac187cebd76878e0b63e9e442356
ccc2d3733d2d5b86d47d9a56346d29d67af4dbbb44be03c8dc3a202b991bf14a
cec238ecad0a131a0bd55bd689b65111dc06f2b1e09ee3e5705703fb8150eb1a
d00cd78c047fda1e6ca040adfb5e0b6aaabe8121122bba319ee201ec3b6e6229
d02a4923bec395c20d1ac91484d059e346aeee0ea43298728d18b092fab2b10e
d36b373b44b77f016e4b7df913ba2da2a8025456f016bc794861f210c0e3ada3
d5e2f62ecf79fe8c13c9c4f8d9db8519103471b851b1584a2796c9da2fb133e3
dd37a1d3fa6a25dd938360e9a100aa83eda0d2a03fef9ba47c05a49322fcf3bd
ddc91dae327d050a1d7fc5ce064d230cbbe15ff166f6fc2dbf4aad3c3b9a5d4a
e24d0437ba28978001a456d280cc41b91109f59f70b9214d182d087801a139b1
e40f65481ad4bc0e042c6f3dbe6d011f05fe84e5a5921962f5a8f32c84b8e999
e42a88444448ac3d60549cc7c1ff2c8a9cac721034c073d80a14a44e79730cca
f92cf61bf974ee2c2078515620ae5248b68c5839732e8d1d191e4aae472d69f1
f9c50e5447b56d620094eb431a7bab452ccf63982dbbae962879a13e93b377ca
fbd904b363a512eda8d026fcdd519239916170a2b695d4992857def0c0fe7fb8
fe52d0b49cc669064847910762a08876f446391e3e4f6490bc37118e06a77927
ffc7a4e596f5e8447cc6824222c142439023beecbea10da9aaf02c1078f8bd66