URL:
https://qqtotokiwi.site/ 1yr old
Submission: On July 19 via api (July 19th 2025, 8:33:15 pm UTC) from US — Scanned from SG

Summary

This website contacted 21 IPs in 4 countries across 18 domains to perform 257 HTTP transactions. The main IP is 92.243.74.2, located in Singapore and belongs to CLOUDFLARESPECTRUM Cloudflare London, LLC, US. The main domain is qqtotokiwi.site. 1yr old
TLS certificate: Issued by WE1 on July 19th 2025. Valid for: 3mo.
This is the only time qqtotokiwi.site was scanned on urlscan.io!

urlscan.io Verdict: No classification

Domain & IP information

IP Address AS Autonomous System
1 72 92.243.74.2 92.243.74.2 209242 (CLOUDFLAR...) (CLOUDFLARESPECTRUM Cloudflare London)
1 64.233.170.97 64.233.170.97 15169 (GOOGLE) (GOOGLE)
132 172.217.194.132 172.217.194.132 15169 (GOOGLE) (GOOGLE)
2 104.21.48.1 104.21.48.1 13335 (CLOUDFLAR...) (CLOUDFLARENET)
3 104.18.16.236 104.18.16.236 13335 (CLOUDFLAR...) (CLOUDFLARENET)
2 2 104.21.19.4 104.21.19.4 13335 (CLOUDFLAR...) (CLOUDFLARENET)
1 104.16.79.73 104.16.79.73 13335 (CLOUDFLAR...) (CLOUDFLARENET)
22 184.51.6.218 184.51.6.218 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.)
1 142.251.10.94 142.251.10.94 15169 (GOOGLE) (GOOGLE)
1 23.58.144.63 23.58.144.63 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.)
4 23.32.29.106 23.32.29.106 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.)
1 172.64.145.29 172.64.145.29 13335 (CLOUDFLAR...) (CLOUDFLARENET)
6 172.67.162.223 172.67.162.223 13335 (CLOUDFLAR...) (CLOUDFLARENET)
1 142.251.10.113 142.251.10.113 15169 (GOOGLE) (GOOGLE)
1 78.46.22.9 78.46.22.9 24940 (HETZNER-A...) (HETZNER-AS Hetzner Online GmbH)
2 199.232.44.157 199.232.44.157 54113 (FASTLY) (FASTLY)
1 162.159.140.229 162.159.140.229 13335 (CLOUDFLAR...) (CLOUDFLARENET)
1 125.56.219.3 125.56.219.3 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.)
1 104.18.24.163 104.18.24.163 13335 (CLOUDFLAR...) (CLOUDFLARENET)
1 96.17.96.8 96.17.96.8 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.)
1 23.197.85.189 23.197.85.189 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.)
257 21
Apex Domain
Subdomains
Transfer
132 googleusercontent.com
blogger.googleusercontent.com — Cisco Umbrella Rank: 10304 9yr old
25 MB
72 qqtotokiwi.site 1 redirects
qqtotokiwi.site 1yr old
488 KB
28 livechatinc.com
cdn.livechatinc.com — Cisco Umbrella Rank: 5282 13yr old
api.livechatinc.com — Cisco Umbrella Rank: 4818 7yr old
secure.livechatinc.com — Cisco Umbrella Rank: 6040 10yr old
accounts.livechatinc.com — Cisco Umbrella Rank: 7098 8yr old
403 KB
6 imgku.io
imgku.io — Cisco Umbrella Rank: 34262 3yr old
30 KB
3 twitter.com
platform.twitter.com — Cisco Umbrella Rank: 1676 13yr old
syndication.twitter.com — Cisco Umbrella Rank: 2016 13yr old
132 KB
3 cloudstoragesharingservice.com
object-d001-cloud.cloudstoragesharingservice.com — Cisco Umbrella Rank: 36015 3yr old
239 KB
2 landingsplash.xyz 2 redirects
landingsplash.xyz — Cisco Umbrella Rank: 46171 10yr old
1 KB
2 shareservice.net
shareservice.net — Cisco Umbrella Rank: 27414 1yr old
204 KB
1 livechat-files.com
cdn.livechat-files.com — Cisco Umbrella Rank: 21608 6yr old
27 KB
1 gyazo.com
i.gyazo.com — Cisco Umbrella Rank: 30215 10yr old
2 KB
1 freeiconspng.com
www.freeiconspng.com — Cisco Umbrella Rank: 146085 10yr old
17 KB
1 google-analytics.com
www.google-analytics.com — Cisco Umbrella Rank: 80 13yr old
1 areabermain.club
cdn.areabermain.club — Cisco Umbrella Rank: 39411 7yr old
1014 KB
1 flaticon.com
cdn-icons-png.flaticon.com — Cisco Umbrella Rank: 40627 5yr old
16 KB
1 gstatic.com
fonts.gstatic.com 10yr old
31 KB
1 cloudflareinsights.com
static.cloudflareinsights.com — Cisco Umbrella Rank: 633 7yr old
7 KB
1 googletagmanager.com
www.googletagmanager.com — Cisco Umbrella Rank: 67 13yr old
134 KB
0 digitaloceanspaces.com Failed
masuk.sgp1.cdn.digitaloceanspaces.com Failed 3yr old
257 18
Domain Requested by
132 blogger.googleusercontent.com qqtotokiwi.site
72 qqtotokiwi.site 1 redirects qqtotokiwi.site
static.cloudflareinsights.com
22 cdn.livechatinc.com qqtotokiwi.site
secure.livechatinc.com
cdn.livechatinc.com
6 imgku.io qqtotokiwi.site
4 api.livechatinc.com cdn.livechatinc.com
3 object-d001-cloud.cloudstoragesharingservice.com qqtotokiwi.site
2 platform.twitter.com qqtotokiwi.site
platform.twitter.com
2 landingsplash.xyz 2 redirects
2 shareservice.net qqtotokiwi.site
1 cdn.livechat-files.com
1 accounts.livechatinc.com cdn.livechatinc.com
1 i.gyazo.com qqtotokiwi.site
1 secure.livechatinc.com cdn.livechatinc.com
1 syndication.twitter.com platform.twitter.com
1 www.freeiconspng.com qqtotokiwi.site
1 www.google-analytics.com www.googletagmanager.com
1 cdn.areabermain.club qqtotokiwi.site
1 cdn-icons-png.flaticon.com qqtotokiwi.site
1 fonts.gstatic.com qqtotokiwi.site
1 static.cloudflareinsights.com qqtotokiwi.site
1 www.googletagmanager.com qqtotokiwi.site
0 masuk.sgp1.cdn.digitaloceanspaces.com Failed qqtotokiwi.site
257 22

This site contains links to these domains. Also see Links.

Domain
rtp.qqtoto.site
t.ly
Subject Issuer Validity Valid
qqtotokiwi.site
WE1
2025-07-19 -
2025-10-17
3mo crt.sh
*.google-analytics.com
WR2
2025-06-23 -
2025-09-15
3mo crt.sh
*.googleusercontent.com
WR2
2025-06-23 -
2025-09-15
3mo crt.sh
shareservice.net
WE1
2025-06-06 -
2025-09-04
3mo crt.sh
cloudstoragesharingservice.com
WE1
2025-06-03 -
2025-09-01
3mo crt.sh
cloudflareinsights.com
WE1
2025-06-25 -
2025-09-23
3mo crt.sh
livechat.com
DigiCert Global G3 TLS ECC SHA384 2020 CA1
2025-06-11 -
2026-06-11
1yr crt.sh
*.gstatic.com
WR2
2025-06-23 -
2025-09-15
3mo crt.sh
*.flaticon.com
E6
2025-07-03 -
2025-10-01
3mo crt.sh
areabermain.club
E5
2025-07-02 -
2025-09-30
3mo crt.sh
imgku.io
WE1
2025-06-20 -
2025-09-18
3mo crt.sh
freeiconspng.com
E6
2025-06-21 -
2025-09-19
3mo crt.sh
*.twimg.com
R11
2025-06-22 -
2025-09-20
3mo crt.sh
twitter.com
E6
2025-06-25 -
2025-09-23
3mo crt.sh
gyazo.com
WE1
2025-07-19 -
2025-10-17
3mo crt.sh

This page contains 4 frames:

Primary Page: https://qqtotokiwi.site/
Frame ID: 85A4B503F3D5E291E896F0483558E49B
Requests: 231 HTTP requests in this frame

Frame: https://qqtotokiwi.site/cdn-cgi/challenge-platform/h/g/scripts/jsd/4d127ba5149d/main.js
Frame ID: 1D7B0FFDFFB7570C7F27DD022EFF7BAD
Requests: 2 HTTP requests in this frame

Frame: https://platform.twitter.com/widgets/widget_iframe.2f70fb173b9000da126c79afe2098f02.html?origin=https%3A%2F%2Fqqtotokiwi.site
Frame ID: 05D033F5323AAD05C5DD0C9B1B513BA9
Requests: 2 HTTP requests in this frame

Frame: https://secure.livechatinc.com/customer/action/open_chat?license_id=15132858&group=0&embedded=1&widget_version=3&unique_groups=0&organizationId=9f4cf5ff-55c6-4c3d-a633-74ba3c34a52b&use_parent_storage=1&x-region=us-south1
Frame ID: EEBA83136233561D3DEBD0C0ABE07EDD
Requests: 22 HTTP requests in this frame

Screenshot

Page Title

QQTOTO : the best place to play online slot and casino games in Indonesia 2025

Detected technologies

(UI frameworks)
Overall confidence: 100%
Detected patterns
  • <link[^>]* href=[^>]*?bootstrap(?:[^>]*?([0-9a-fA-F]{7,40}|[\d]+(?:.[\d]+(?:.[\d]+)?)?)|)[^>]*?(?:\.min)?\.css
  • bootstrap(?:[^>]*?([0-9a-fA-F]{7,40}|[\d]+(?:.[\d]+(?:.[\d]+)?)?)|)[^>]*?(?:\.min)?\.js

(Web frameworks)
Overall confidence: 100%
Detected patterns

(UI frameworks)
Overall confidence: 100%
Detected patterns
  • <link [^>]+(?:/([\d.]+)/)?animate\.(?:min\.)?css

(JavaScript frameworks)
Overall confidence: 100%
Detected patterns
  • <link rel="amphtml"

(Analytics)
Overall confidence: 100%
Detected patterns
  • static\.cloudflareinsights\.com/beacon(?:\.min)?\.js

(Font scripts)
Overall confidence: 100%
Detected patterns
  • <link[^>]* href=[^>]+(?:([\d.]+)/)?(?:css/)?font-awesome(?:\.min)?\.css
  • <link[^>]* href=[^>]*?(?:F|f)o(?:n|r)t-?(?:A|a)wesome(?:[^>]*?([0-9a-fA-F]{7,40}|[\d]+(?:.[\d]+(?:.[\d]+)?)?)|)
  • (?:F|f)o(?:n|r)t-?(?:A|a)wesome(?:.*?([0-9a-fA-F]{7,40}|[\d]+(?:.[\d]+(?:.[\d]+)?)?)|)

(Analytics)
Overall confidence: 100%
Detected patterns

(Tag managers)
Overall confidence: 100%
Detected patterns
  • googletagmanager\.com/gtag/js

(JavaScript libraries)
Overall confidence: 100%
Detected patterns
  • <link [^>]*href="[^"]+lightbox(?:\.min)?\.css
  • lightbox(?:-plus-jquery)?.{0,32}\.js

(Live chat)
Overall confidence: 100%
Detected patterns
  • cdn\.livechatinc\.com/.*tracking\.js

(JavaScript libraries)
Overall confidence: 100%
Detected patterns
  • ([\d.]+)?/modernizr(?:\.([\d.]+))?.*\.js

(JavaScript libraries)
(Widgets)
Overall confidence: 100%
Detected patterns
  • //platform\.twitter\.com/widgets\.js

(JavaScript libraries)
Overall confidence: 100%
Detected patterns
  • jquery[.-]([\d.]*\d)[^/]*\.js
  • jquery.*\.js(?:\?ver(?:sion)?=([\d.]+))?

Page Statistics

257
Requests

98 %
HTTPS

0 %
IPv6

18
Domains

22
Subdomains

21
IPs

4
Countries

27997 kB
Transfer

30000 kB
Size

15
Cookies

Redirected requests

There were HTTP redirect chains for the following requests:

Request Chain 34
  • https://landingsplash.xyz/banner/image/promotion/IDNTOTOSYD.jpg HTTP 301
  • https://object-d001-cloud.cloudstoragesharingservice.com/banner/image/promotion/IDNTOTOSYD.jpg
Request Chain 35
  • https://landingsplash.xyz/banner/image/promotion/IDNTOTTOHK.jpg HTTP 301
  • https://object-d001-cloud.cloudstoragesharingservice.com/banner/image/promotion/IDNTOTTOHK.jpg
Request Chain 221
  • https://qqtotokiwi.site/cdn-cgi/challenge-platform/scripts/jsd/main.js HTTP 302
  • https://qqtotokiwi.site/cdn-cgi/challenge-platform/h/g/scripts/jsd/4d127ba5149d/main.js

257 HTTP transactions
0 data transactions

Method
Protocol
Status Resource
Path
Size
x-fer
Time
Latency
Type
MIME-Type
IP
Location
GET
H2
200
Primary Request / Show response
qqtotokiwi.site/
243 KB
56 KB
172ms
135ms
Document
text/html
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
81f2e2a5c8a7ddaecc142e943f0cc8ecff171c000576f7ce2975c3440565d24f

Request headers

Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36

Response headers

age
0
cache-control
public, s-maxage=900
cf-cache-status
DYNAMIC
cf-ray
961cfe2c2c3a3e06-SIN
content-encoding
gzip
content-type
text/html; charset=UTF-8
date
Sat, 19 Jul 2025 20:33:16 GMT
server
cloudflare
server-timing
cfCacheStatus;desc="DYNAMIC" cfOrigin;dur=0,cfEdge;dur=130
vary
Accept-Encoding
x-cache
MISS
x-cache-hits
0
x-cacheable
1
GET
H2
200
bootstrap.min.css
qqtotokiwi.site/assets/css/vendor/bootstrap/
107 KB
18 KB
31ms
29ms
Stylesheet
text/css
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/css/vendor/bootstrap/bootstrap.min.css
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
1100977a241133f42972e197c28a12254b88b7b512eb3f4a8d79f3d7ef8a0084

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"67a03711-1aaeb"
cf-ray
961cfe2d1cc33e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
text/css
last-modified
Mon, 03 Feb 2025 03:25:05 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
font-awesome.min.css
qqtotokiwi.site/assets/css/
30 KB
7 KB
21ms
20ms
Stylesheet
text/css
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/css/font-awesome.min.css
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
799aeb25cc0373fdee0e1b1db7ad6c2f6a0e058dfadaa3379689f583213190bd

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"650bf9d0-7918"
cf-ray
961cfe2d1cc43e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
text/css
last-modified
Thu, 21 Sep 2023 08:07:44 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
animate.min.css
qqtotokiwi.site/assets/css/vendor/animate/
41 KB
3 KB
23ms
23ms
Stylesheet
text/css
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/css/vendor/animate/animate.min.css
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
e5fbca3a78b54f9bf7ef5a205a5d6264b74e8026943ce6523b214d4bacf78761

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"650bf9d0-a29b"
cf-ray
961cfe2d1cc53e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
text/css
last-modified
Thu, 21 Sep 2023 08:07:44 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
bootstrap-checkbox.min.css
qqtotokiwi.site/assets/css/vendor/
7 KB
1 KB
26ms
16ms
Stylesheet
text/css
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/css/vendor/bootstrap-checkbox.min.css
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
bcc36e6dfb15f4c5b87dff41e7f4007cc49b1bd0c460ac5d5e818b4e3a97b2cb

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"650bf9d0-1a50"
cf-ray
961cfe2d2cca3e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
text/css
last-modified
Thu, 21 Sep 2023 08:07:44 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
3d-corner-ribbons.min.css
qqtotokiwi.site/assets/css/vendor/ribbons/
5 KB
1 KB
30ms
20ms
Stylesheet
text/css
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/css/vendor/ribbons/3d-corner-ribbons.min.css
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
7cf0b8467b88360e4e11881a231c013464a4fe2c449887baa7fde731a7058845

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"650bf9d0-14f6"
cf-ray
961cfe2d2ccc3e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
text/css
last-modified
Thu, 21 Sep 2023 08:07:44 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
simpletextrotator.min.css
qqtotokiwi.site/assets/js/vendor/text-rotator/css/
3 KB
552 B
33ms
24ms
Stylesheet
text/css
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/js/vendor/text-rotator/css/simpletextrotator.min.css
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
e58260e204b97def3d0cb7c8f11c0ddb7e2255eb43f20c05cd9578dd3b6a31d9

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"6466f3b1-b3f"
cf-ray
961cfe2d2ccd3e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
text/css
last-modified
Fri, 19 May 2023 03:57:37 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
tabdrop.min.css
qqtotokiwi.site/assets/js/vendor/tabdrop/css/
197 B
267 B
29ms
21ms
Stylesheet
text/css
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/js/vendor/tabdrop/css/tabdrop.min.css
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
61e4384b213f36a3a7fc08b44510fd439ecf3c8523b8633f723fb1012d2fbfbf

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"6466f3b1-c5"
cf-ray
961cfe2d2cce3e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
text/css
last-modified
Fri, 19 May 2023 03:57:37 GMT
x-cache-hits
0
server
cloudflare
vary
Accept-Encoding
GET
H2
200
fonts.min.css
qqtotokiwi.site/assets/css/
3 KB
824 B
32ms
23ms
Stylesheet
text/css
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/css/fonts.min.css
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
9531877a395471eb20e85f9e742bf48cde70d1e528d9aaa55c1c210fb3dbf811

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"650bf9d0-cc4"
cf-ray
961cfe2d2ccf3e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
text/css
last-modified
Thu, 21 Sep 2023 08:07:44 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
owl.carousel.min.css
qqtotokiwi.site/assets/js/vendor/owl-carousel/css/
1 KB
480 B
31ms
22ms
Stylesheet
text/css
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/js/vendor/owl-carousel/css/owl.carousel.min.css
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
6f78df7d3286f40fde31a16161673e4ea46ccc4fd7845eb84f5e9eb4219f235d

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"6466f3b1-48a"
cf-ray
961cfe2d2cd33e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
397
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
text/css
last-modified
Fri, 19 May 2023 03:57:37 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
owl.theme.min.css
qqtotokiwi.site/assets/js/vendor/owl-carousel/css/
1 KB
495 B
42ms
34ms
Stylesheet
text/css
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/js/vendor/owl-carousel/css/owl.theme.min.css
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
f0a11eb1d8fabf95360258de73cf1cd91360c3b97c1ba92d7744e5eaa40f49d1

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"6466f3b1-460"
cf-ray
961cfe2d2cd43e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
text/css
last-modified
Fri, 19 May 2023 03:57:37 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
owl.transitions.min.css
qqtotokiwi.site/assets/js/vendor/owl-carousel/css/
4 KB
650 B
42ms
34ms
Stylesheet
text/css
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/js/vendor/owl-carousel/css/owl.transitions.min.css
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
df344411eb3c7585c6398e1b38475fcc3040ccdc4007ed707734d46e3a50843e

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"6466f3b1-e73"
cf-ray
961cfe2d2cd63e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
text/css
last-modified
Fri, 19 May 2023 03:57:37 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
nivo-lightbox.min.css
qqtotokiwi.site/assets/js/vendor/nivo-lightbox/css/
4 KB
903 B
34ms
27ms
Stylesheet
text/css
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/js/vendor/nivo-lightbox/css/nivo-lightbox.min.css
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
75beb6ea66cfacbbad808671aa6b753ef5c5bf4e8d5efb9adf9cb840379ed803

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"6466f3b1-119d"
cf-ray
961cfe2d2cd73e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
text/css
last-modified
Fri, 19 May 2023 03:57:37 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
default.min.css
qqtotokiwi.site/assets/js/vendor/nivo-lightbox/css/themes/default/
2 KB
689 B
49ms
42ms
Stylesheet
text/css
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/js/vendor/nivo-lightbox/css/themes/default/default.min.css
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
bdb49593241ac3b4ffa1a72798effc086924f32ee7ae14c27002c9ff32600090

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"6466f3b1-8de"
cf-ray
961cfe2d2cd83e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
text/css
last-modified
Fri, 19 May 2023 03:57:37 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
bank.min.css
qqtotokiwi.site/css/
5 KB
1 KB
36ms
29ms
Stylesheet
text/css
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/css/bank.min.css
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
ce416742adf00033170694298361d4824de9c49c9c0f66137190811ee11e53f6

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"6466f3b1-1315"
cf-ray
961cfe2d2cdb3e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
text/css
last-modified
Fri, 19 May 2023 03:57:37 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
shio_svg.min.css
qqtotokiwi.site/css/
2 KB
315 B
31ms
25ms
Stylesheet
text/css
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/css/shio_svg.min.css
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
c3d46f64e06d98e5d467a140ac28d8fe3f17eeb0b05f6afbf3a4742bfbe48581

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"6466f3b1-6b4"
cf-ray
961cfe2d2cdc3e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
text/css
last-modified
Fri, 19 May 2023 03:57:37 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
marquee.css
qqtotokiwi.site/css/
2 KB
746 B
34ms
28ms
Stylesheet
text/css
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/css/marquee.css?v=c3syfye1yivoif3u4mel
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
2d2a7ab1708e5aeee4123d037d8484e9e4c3cca489b4b6b3b931143911403134

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"6466f3b1-89f"
cf-ray
961cfe2d2cde3e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
text/css
last-modified
Fri, 19 May 2023 03:57:37 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
bsq2.css
qqtotokiwi.site/assets/css/bsq/
96 KB
13 KB
57ms
51ms
Stylesheet
text/css
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/css/bsq/bsq2.css
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
034ae3152431795278b88fd9ecc51ccdd6ff6f3be0f482cb741c82ee39b99cc9

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"650bf9cf-181a2"
cf-ray
961cfe2d2cdf3e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
text/css
last-modified
Thu, 21 Sep 2023 08:07:43 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
game_compressed_ic.min.css
qqtotokiwi.site/assets/css/
2 KB
560 B
35ms
30ms
Stylesheet
text/css
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/css/game_compressed_ic.min.css
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
544b151ad8c7487ebcaa8538d1c3c18b2a100720d6fe9ef6ab74fa93d5c638b6

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"650bf9d0-996"
cf-ray
961cfe2d2ce03e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
text/css
last-modified
Thu, 21 Sep 2023 08:07:44 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
defaultTheme.min.css
qqtotokiwi.site/assets/css/
1 KB
586 B
54ms
49ms
Stylesheet
text/css
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/css/defaultTheme.min.css
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
e8a7b2ed05fcc0a064737d127e166f8e81781b746b70d8e9aeff7ad0b055464c

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"650bf9d0-49c"
cf-ray
961cfe2d2ce13e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
text/css
last-modified
Thu, 21 Sep 2023 08:07:44 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
style.min.css
qqtotokiwi.site/assets/css/
1 KB
638 B
46ms
41ms
Stylesheet
text/css
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/css/style.min.css
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
41394d817f909ea1d7d35a3652e3d1a661731ba3380312d55f637cb9b5de7c70

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"650bf9d0-545"
cf-ray
961cfe2d2ce33e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
text/css
last-modified
Thu, 21 Sep 2023 08:07:44 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
jquery-2.2.4.min.js Show response
qqtotokiwi.site/assets/js/
84 KB
29 KB
55ms
51ms
Script
application/javascript
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/js/jquery-2.2.4.min.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
fdce77a6d0053f32d231518a84a71bcab5c86045ed52369da00b89d4284aef46

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"6466f3b1-14e49"
cf-ray
961cfe2d2ce53e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
application/javascript
last-modified
Fri, 19 May 2023 03:57:37 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
additional.css
qqtotokiwi.site/assets/css/
10 KB
2 KB
54ms
50ms
Stylesheet
text/css
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/css/additional.css
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
2b735a9ab21e15a9f70552ac4d1f479b4df7bf5161a07c1bbee610e00798c3f4

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"650bf9ce-299f"
cf-ray
961cfe2d2ce43e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
text/css
last-modified
Thu, 21 Sep 2023 08:07:42 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
feedback2.png
qqtotokiwi.site/assets/img/
1 KB
1 KB
29ms
26ms
Image
image/png
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/img/feedback2.png
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
639775068932c1b628a731e51f57a420b6006929bf08058d1dd628b2b0aa1e51

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cache-control
public, max-age=2592000
cf-cache-status
MISS
etag
"650bd9bd-49c"
cf-ray
961cfe2d2ce63e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
1180
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
image/png
last-modified
Thu, 21 Sep 2023 05:50:53 GMT
x-cache-hits
0
server
cloudflare
vary
Accept-Encoding
GET
H2
200
vbulletin_md5.js Show response
qqtotokiwi.site/js/
6 KB
2 KB
33ms
30ms
Script
application/javascript
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/js/vbulletin_md5.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
94a03d94ea079e4a5877a8d14914288246f30a12b3833c8d59ad22dffc63a7d1

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"6466f3b1-1639"
cf-ray
961cfe2d2ce83e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
application/javascript
last-modified
Fri, 19 May 2023 03:57:37 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
loader.gif
qqtotokiwi.site/mobile/assets/img/
5 KB
6 KB
25ms
24ms
Image
image/gif
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/mobile/assets/img/loader.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
a76090f2d604a7e9bd429900001b367ae94f52d749fd0f94706be887d87cce7f

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cache-control
public, max-age=2592000
cf-cache-status
MISS
etag
"6466f3b2-158d"
cf-ray
961cfe2d9d183e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
5517
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
image/gif
last-modified
Fri, 19 May 2023 03:57:38 GMT
x-cache-hits
0
server
cloudflare
vary
Accept-Encoding
GET
H2
200
js Show response
www.googletagmanager.com/gtag/
393 KB
134 KB
100ms
39ms
Script
application/javascript
64.233.170.97
GOOGLE
General
Full URL
https://www.googletagmanager.com/gtag/js?id=G-SSN8YGQCHV
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
64.233.170.97 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
sg-in-f97.1e100.net
Software
Google Tag Manager /
Resource Hash
38052b1a4b563ee810478ffba5f8e43545d8c3c2c91c1b35a5a652498eb406d9
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

content-encoding
zstd
report-to
{"group":"ascgcycc:1077:0","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/scaffolding/ascgcycc:1077:0"}],}
expires
Sat, 19 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
access-control-allow-headers
Cache-Control
strict-transport-security
max-age=31536000; includeSubDomains
cache-control
private, max-age=900
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
content-security-policy-report-only
script-src 'none'; form-action 'none'; frame-src 'none'; report-uri https://csp.withgoogle.com/csp/scaffolding/ascgcycc:1077:0
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to=ascgcycc:1077:0
content-length
136623
x-xss-protection
0
server
Google Tag Manager
GET
H2
200
rtp%20(1).gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEieyl0BGEJRM-OEpZo6Vw3VaW2ufmQ7oYTb6TP20EC_N_E35__UYXMWes_BBpc8PU9F6AJxLHlV0kT9ukphY6ackurtZyirtTrs7bcRiLPsjc9kM9yCmYxDepByvPOvQBWDtO8h9Eso_X7L1TyM...
955 KB
956 KB
317ms
264ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEieyl0BGEJRM-OEpZo6Vw3VaW2ufmQ7oYTb6TP20EC_N_E35__UYXMWes_BBpc8PU9F6AJxLHlV0kT9ukphY6ackurtZyirtTrs7bcRiLPsjc9kM9yCmYxDepByvPOvQBWDtO8h9Eso_X7L1TyMyElgCL47TpE_6cvEjPVBsIOyN7afxHSnFZRyYK2scZw/s16000/rtp%20(1).gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
f5d06911ad2428743c7145836cd0bbe00bc78de44e0bf68637c98ad2dc9cd3fa
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v1ca"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
977882
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="rtp (1).gif"
GET
H2
200
baner%20mahyong%20.jpeg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjP9LIBPaSZNK9-shbmbFRE9TL-3s_8wOKV_fEKHXrJ_W4kQa3pYeKWKjpDqUwtDIzxlmXlKInwxtH2em4MizRj2XKNF2JW6Nnh2yiMcvIFid7TYWxgIrI77AGh0ywfNsnhNm8O_8kMxUPWG6e9...
146 KB
147 KB
281ms
263ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjP9LIBPaSZNK9-shbmbFRE9TL-3s_8wOKV_fEKHXrJ_W4kQa3pYeKWKjpDqUwtDIzxlmXlKInwxtH2em4MizRj2XKNF2JW6Nnh2yiMcvIFid7TYWxgIrI77AGh0ywfNsnhNm8O_8kMxUPWG6e9bXDUQKo7CXcf6biBBYUfETG4b6lqDRswG3KS5Z0Qs5A/s16000/baner%20mahyong%20.jpeg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
09fdb0950475d742154da396ed6d6591b899bc7791798554c47cd5ad8fae1087
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v3f5"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
149792
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="baner mahyong .jpeg"
GET
H2
200
qqtoto44.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEi07EN_TjIm_29R42ERjSwsrzvPBKtbCkpXtB4H1rWrCmn0Etll49BBdA1EpL0F0DQJGcT4-ulngGpcqBmgbgZWR4JqJyBEUw9A8wC-kjHxO2iKMEYzaUvsb7GK7C6AANgLsWCpGFCCZpjErFDu...
390 KB
390 KB
289ms
235ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEi07EN_TjIm_29R42ERjSwsrzvPBKtbCkpXtB4H1rWrCmn0Etll49BBdA1EpL0F0DQJGcT4-ulngGpcqBmgbgZWR4JqJyBEUw9A8wC-kjHxO2iKMEYzaUvsb7GK7C6AANgLsWCpGFCCZpjErFDugtdQZx1MxW6wRVHQfj6NX6DWTm6zdLN2TMpazLLRXOg/s16000/qqtoto44.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
a5ea9024d51dc1611dfb718849b48c24e6a09114c0da31995f58551326074b57
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v9f"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
398872
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="qqtoto44.jpg"
GET
H2
200
qqtoto5.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEg-PzF-HeMpp2KmvUzQVvcyOI4YsVqcXpQZIXwAePz1LKOTA7UjxURlBgR2oKkQy1dVcwfTECtE1dlaKfXMfNX2XqGZbpgwBa9oDoho8LLxjBf5Fi6OAZd83SpU5XbNwUzrcF7Hgbk4ld-RXsLh...
417 KB
417 KB
272ms
221ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEg-PzF-HeMpp2KmvUzQVvcyOI4YsVqcXpQZIXwAePz1LKOTA7UjxURlBgR2oKkQy1dVcwfTECtE1dlaKfXMfNX2XqGZbpgwBa9oDoho8LLxjBf5Fi6OAZd83SpU5XbNwUzrcF7Hgbk4ld-RXsLhpghRRor3oGapNFgpl2CRlvOyGIf3pZ6viHKTTwp7Iao/s16000/qqtoto5.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
3c1fac4135f8cc39b41d72462949f6a3852301c5aa228b0e372f3eaeba477b17
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v9f"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
426597
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="qqtoto5.jpg"
GET
H2
200
qqtoto2.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhd-YNX16Fr0SJq4E6uQqxWZiGGXvgjmrKFxj86T_YpAV92YPVY9QM_vHLdMDjY9fp_94s9FOUjoaDWLYto8AlY2RmfIaCE9sniUrrw06p9Gksu2UsrNwc4RhNi87OjIfTj7Qy_tMHxF2UkMlbD...
336 KB
336 KB
302ms
249ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhd-YNX16Fr0SJq4E6uQqxWZiGGXvgjmrKFxj86T_YpAV92YPVY9QM_vHLdMDjY9fp_94s9FOUjoaDWLYto8AlY2RmfIaCE9sniUrrw06p9Gksu2UsrNwc4RhNi87OjIfTj7Qy_tMHxF2UkMlbDQ9zyqXFX4OF1CA32H070DKX185k-5SGYOCsZ8INdvw4/s16000/qqtoto2.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
eb031bb8465ecf1226855bddd88351d72ba66157d0330964d7a5f41e2ab04ea9
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v9f"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
343712
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="qqtoto2.jpg"
GET
H2
200
qqtoto3.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgyID9Rty8LwA6e0VhX1RqM4VsU-8rWeXN8iQ5qxEWsWg76Llec1Ym73GVA7JujE-45ly4rizHyk5Ia0K5o5agCODfD1IdhQQ9zoqUg04niyIvi57diI6xN0wO4opK1FrVGUgo6c-kF3Qvz1wIc...
370 KB
370 KB
336ms
283ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgyID9Rty8LwA6e0VhX1RqM4VsU-8rWeXN8iQ5qxEWsWg76Llec1Ym73GVA7JujE-45ly4rizHyk5Ia0K5o5agCODfD1IdhQQ9zoqUg04niyIvi57diI6xN0wO4opK1FrVGUgo6c-kF3Qvz1wIc0X3fLe4qHU3vTucwHr4OZSYbWALXFqHSk_kRD3gw018/s16000/qqtoto3.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
5143d80cb7714a2fa2526dbba0870b76bb3255e035f5d7c4bc197599562e0cf0
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v9f"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
378636
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="qqtoto3.jpg"
GET
H3
200
Slide-Banner-Homepage---840-x-480-px.jpg
shareservice.net/banner/image/banner/
104 KB
105 KB
120ms
60ms
Image
image/jpeg
104.21.48.1
CLOUDFLARENET
General
Full URL
https://shareservice.net/banner/image/banner/Slide-Banner-Homepage---840-x-480-px.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.21.48.1 , Ascension Island, ASN13335 (CLOUDFLARENET, US),
Reverse DNS
Software
cloudflare /
Resource Hash
b9506d56c2cd3db1ccf10c95c053d7efc6cf5199baee34cdcba665d1ed7542f4
Security Headers
Name Value
X-Frame-Options SAMEORIGIN

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cf-cache-status
HIT
etag
"6868b3f3-19f99"
age
5222
report-to
{"endpoints":[{"url":"https:\/\/a.nel.cloudflare.com\/report\/v4?s=5myyph9kb2zJ0KKJIAljqRq4kza%2FUYmiNTVNlaoczVnjychVjeUsOYT9hsv9IHXhw8HgMcfPGKx8I88vSiTWHCyRFO%2FF89P4yQyU57WxG0DByx1DrLONJDDFVcaHsnhNAJIz"}],"group":"cf-nel","max_age":604800}
alt-svc
h3=":443"; ma=86400
server-timing
cfL4;desc="?proto=QUIC&rtt=4559&min_rtt=3436&rtt_var=2868&sent=14&recv=11&lost=0&retrans=1&sent_bytes=8937&recv_bytes=3679&delivery_rate=649324&ss_exit_cwnd=0&ss_exit_reason=0&cwnd=15427&unsent_bytes=0&cid=56750bf3ab033f3f&ts=34&inflight_dur=33&x=103"
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
image/jpeg
vary
Accept-Encoding
last-modified
Sat, 05 Jul 2025 05:11:15 GMT
x-frame-options
SAMEORIGIN
cache-control
max-age=5356800
nel
{"success_fraction":0,"report_to":"cf-nel","max_age":604800}
cf-ray
961cfe2e59edfda7-SIN
accept-ranges
bytes
content-length
106393
server
cloudflare
GET
H2
200
photo_2024-01-17_15-12-52.jpg
object-d001-cloud.cloudstoragesharingservice.com/banner/image/banner/
64 KB
64 KB
100ms
39ms
Image
image/jpeg
104.18.16.236
CLOUDFLARENET
General
Full URL
https://object-d001-cloud.cloudstoragesharingservice.com/banner/image/banner/photo_2024-01-17_15-12-52.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.18.16.236 , Ascension Island, ASN13335 (CLOUDFLARENET, US),
Reverse DNS
Software
cloudflare /
Resource Hash
494e58831398fac29d99b39418c070bd8a06f997c84b222a59003da9f0771168
Security Headers
Name Value
X-Frame-Options SAMEORIGIN

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cache-control
public, max-age=14400
cf-bgj
h2pri
etag
"6702d5e5-fe84"
age
2867
cf-cache-status
HIT
cf-ray
961cfe2e5e17401a-SIN
expires
Sun, 20 Jul 2025 00:33:16 GMT
accept-ranges
bytes
content-length
65156
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
image/jpeg
last-modified
Sun, 06 Oct 2024 18:24:37 GMT
vary
Accept-Encoding
server
cloudflare
x-frame-options
SAMEORIGIN
GET
H2
200
IDNTOTOSYD.jpg
object-d001-cloud.cloudstoragesharingservice.com/banner/image/promotion/
Redirect Chain
  • https://landingsplash.xyz/banner/image/promotion/IDNTOTOSYD.jpg
  • https://object-d001-cloud.cloudstoragesharingservice.com/banner/image/promotion/IDNTOTOSYD.jpg
88 KB
88 KB
29ms
26ms
Image
image/jpeg
104.18.16.236
CLOUDFLARENET
General
Full URL
https://object-d001-cloud.cloudstoragesharingservice.com/banner/image/promotion/IDNTOTOSYD.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Server
104.18.16.236 , Ascension Island, ASN13335 (CLOUDFLARENET, US),
Reverse DNS
Software
cloudflare /
Resource Hash
4e02417535468c9d74f33333ea8aa01ee1921f11cf19de61d1f9b1288ca9019c
Security Headers
Name Value
X-Frame-Options SAMEORIGIN

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cache-control
public, max-age=14400
cf-bgj
h2pri
etag
"670f756d-160d3"
age
5864
cf-cache-status
HIT
cf-ray
961cfe2efe64401a-SIN
expires
Sun, 20 Jul 2025 00:33:16 GMT
accept-ranges
bytes
content-length
90323
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
image/jpeg
last-modified
Wed, 16 Oct 2024 08:12:29 GMT
vary
Accept-Encoding
server
cloudflare
x-frame-options
SAMEORIGIN

Redirect headers

nel
{"success_fraction":0,"report_to":"cf-nel","max_age":604800}
location
https://object-d001-cloud.cloudstoragesharingservice.com/banner/image/promotion/IDNTOTOSYD.jpg
cf-cache-status
HIT
age
1179
cache-control
max-age=14400
report-to
{"endpoints":[{"url":"https:\/\/a.nel.cloudflare.com\/report\/v4?s=ypZ3QA9qczuiv2KuDdwocgaAM8Q8RO8IR5X2cZMu%2B5oCMP8Kp%2BBjJK1dVVqK%2FYB2Azk5mokIAkykFLDOIjY8rUtO0EAiQNPJs7vNIe6QdX4%2F14i5b%2BmWVLg2hSN2fbp9bZ4fpg%3D%3D"}],"group":"cf-nel","max_age":604800}
cf-ray
961cfe2e3f2e5f35-SIN
alt-svc
h3=":443"; ma=86400
server-timing
cfL4;desc="?proto=QUIC&rtt=5159&min_rtt=2950&rtt_var=2843&sent=14&recv=11&lost=0&retrans=0&sent_bytes=4679&recv_bytes=3665&delivery_rate=447018&ss_exit_cwnd=0&ss_exit_reason=0&cwnd=16458&unsent_bytes=0&cid=f72c0f42b2d82d28&ts=55&inflight_dur=38&x=103"
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
text/html
vary
Accept-Encoding
server
cloudflare
GET
H2
200
IDNTOTTOHK.jpg
object-d001-cloud.cloudstoragesharingservice.com/banner/image/promotion/
Redirect Chain
  • https://landingsplash.xyz/banner/image/promotion/IDNTOTTOHK.jpg
  • https://object-d001-cloud.cloudstoragesharingservice.com/banner/image/promotion/IDNTOTTOHK.jpg
87 KB
87 KB
14ms
13ms
Image
image/jpeg
104.18.16.236
CLOUDFLARENET
General
Full URL
https://object-d001-cloud.cloudstoragesharingservice.com/banner/image/promotion/IDNTOTTOHK.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Server
104.18.16.236 , Ascension Island, ASN13335 (CLOUDFLARENET, US),
Reverse DNS
Software
cloudflare /
Resource Hash
cf91122176ba6cadc04f42930dd19b4f8db1b670efcb5b9d8cdc18696e3d1a65
Security Headers
Name Value
X-Frame-Options SAMEORIGIN

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cache-control
public, max-age=14400
cf-bgj
h2pri
etag
"670f756e-15aa8"
age
1400
cf-cache-status
HIT
cf-ray
961cfe2eee5e401a-SIN
expires
Sun, 20 Jul 2025 00:33:16 GMT
accept-ranges
bytes
content-length
88744
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
image/jpeg
last-modified
Wed, 16 Oct 2024 08:12:30 GMT
vary
Accept-Encoding
server
cloudflare
x-frame-options
SAMEORIGIN

Redirect headers

nel
{"success_fraction":0,"report_to":"cf-nel","max_age":604800}
location
https://object-d001-cloud.cloudstoragesharingservice.com/banner/image/promotion/IDNTOTTOHK.jpg
cf-cache-status
HIT
age
1179
cache-control
max-age=14400
report-to
{"endpoints":[{"url":"https:\/\/a.nel.cloudflare.com\/report\/v4?s=hB%2FTfieXJf4B6X48Rb18UIbixmNKvW2ZOi1TgVUgfG6gbWjJi9dfoigeWg2AYA%2BFC2R1k%2FZJ0w2NIfrmcePhrsTqDpeo2SzPhWNgCz29eCo6wc9xzB03Ca%2FRgmy0j59Z817%2F2A%3D%3D"}],"group":"cf-nel","max_age":604800}
cf-ray
961cfe2e3f2f5f35-SIN
alt-svc
h3=":443"; ma=86400
server-timing
cfL4;desc="?proto=QUIC&rtt=5475&min_rtt=3416&rtt_var=2949&sent=12&recv=10&lost=0&retrans=0&sent_bytes=3706&recv_bytes=3622&delivery_rate=447018&ss_exit_cwnd=0&ss_exit_reason=0&cwnd=15485&unsent_bytes=0&cid=f72c0f42b2d82d28&ts=51&inflight_dur=35&x=103"
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
text/html
vary
Accept-Encoding
server
cloudflare
GET
H3
200
Plinko_slide-banner-homepage.jpg
shareservice.net/banner/image/banner/
99 KB
100 KB
116ms
59ms
Image
image/jpeg
104.21.48.1
CLOUDFLARENET
General
Full URL
https://shareservice.net/banner/image/banner/Plinko_slide-banner-homepage.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.21.48.1 , Ascension Island, ASN13335 (CLOUDFLARENET, US),
Reverse DNS
Software
cloudflare /
Resource Hash
d5a2dc8181d675093d1fb20ac43e86ef38bdfd8f1b3326db0da54d12d98158fc
Security Headers
Name Value
X-Frame-Options SAMEORIGIN

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cf-cache-status
HIT
etag
"6868b3e4-18bd4"
age
4977
report-to
{"endpoints":[{"url":"https:\/\/a.nel.cloudflare.com\/report\/v4?s=HH2MsZeZrE2UX%2FsCYi966GT0wXiLaSU%2BxaYcNqHmOmnX76CDB0ZHelQz1TOD3Ay3co3AC%2F%2FUovrJaFKL1Y%2BQDpCIjP85tNFUjromE%2FCYhSIYirM7Kiv1sS6B3v4zxxaheGCV"}],"group":"cf-nel","max_age":604800}
alt-svc
h3=":443"; ma=86400
server-timing
cfL4;desc="?proto=QUIC&rtt=4559&min_rtt=3436&rtt_var=2868&sent=10&recv=11&lost=0&retrans=1&sent_bytes=4137&recv_bytes=3679&delivery_rate=649324&ss_exit_cwnd=0&ss_exit_reason=0&cwnd=15427&unsent_bytes=0&cid=56750bf3ab033f3f&ts=34&inflight_dur=28&x=103"
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
image/jpeg
vary
Accept-Encoding
last-modified
Sat, 05 Jul 2025 05:11:00 GMT
x-frame-options
SAMEORIGIN
cache-control
max-age=5356800
nel
{"success_fraction":0,"report_to":"cf-nel","max_age":604800}
cf-ray
961cfe2e59eefda7-SIN
accept-ranges
bytes
content-length
101332
server
cloudflare
GET
H2
200
icon-pools.jpg
qqtotokiwi.site/assets/img/icon/
7 KB
7 KB
73ms
26ms
Image
image/jpeg
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/img/icon/icon-pools.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
c1af05964be2562a6bbf7c1d8f2a19554198d2e2c1980454a2b8f61f307772ff

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cache-control
public, max-age=2592000
cf-cache-status
MISS
etag
"650bd9bd-1ad6"
cf-ray
961cfe2e3d7d3e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
6870
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
image/jpeg
last-modified
Thu, 21 Sep 2023 05:50:53 GMT
x-cache-hits
0
server
cloudflare
vary
Accept-Encoding
GET
H2
200
icon-hongkong.jpg
qqtotokiwi.site/assets/img/icon/
5 KB
5 KB
83ms
36ms
Image
image/jpeg
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/img/icon/icon-hongkong.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
8b2f204a6ecba604871a339562709f1194ae9ab0a2c8ad61564e4788682b9f2d

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cache-control
public, max-age=2592000
cf-cache-status
MISS
etag
"650bd9bd-1265"
cf-ray
961cfe2e3d7e3e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
4709
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
image/jpeg
last-modified
Thu, 21 Sep 2023 05:50:53 GMT
x-cache-hits
0
server
cloudflare
vary
Accept-Encoding
GET
H2
200
icon-24dspin.jpg
qqtotokiwi.site/assets/img/icon/
5 KB
5 KB
74ms
29ms
Image
image/jpeg
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/img/icon/icon-24dspin.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
bb33c75ebfea05c8a890cf324caa643447aff6ccc845cf1b6877d9d0ed214a61

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cache-control
public, max-age=2592000
cf-cache-status
MISS
etag
"650bd9bd-14db"
cf-ray
961cfe2e3d7f3e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
5339
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
image/jpeg
last-modified
Thu, 21 Sep 2023 05:50:53 GMT
x-cache-hits
0
server
cloudflare
vary
Accept-Encoding
GET
H2
200
icon-dice6.jpg
qqtotokiwi.site/assets/img/icon/
5 KB
5 KB
71ms
27ms
Image
image/jpeg
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/img/icon/icon-dice6.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
d942e4f9b28cd8cfe2961f8a40919d77a8548e8341782c9c129bccfb87dee632

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cache-control
public, max-age=2592000
cf-cache-status
MISS
etag
"66028b10-152d"
cf-ray
961cfe2e3d803e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
5421
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
image/jpeg
last-modified
Tue, 26 Mar 2024 08:45:04 GMT
x-cache-hits
0
server
cloudflare
vary
Accept-Encoding
GET
H2
200
icon-totomacau.jpg
qqtotokiwi.site/assets/img/icon/
51 KB
51 KB
102ms
58ms
Image
image/jpeg
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/img/icon/icon-totomacau.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
44afa7bac070be11a25113dd4ced630691439d7801bb9fbaf0b2251776d1e558

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cache-control
public, max-age=2592000
cf-cache-status
MISS
etag
"66028b10-cd19"
cf-ray
961cfe2e3d813e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
52505
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
image/jpeg
last-modified
Tue, 26 Mar 2024 08:45:04 GMT
x-cache-hits
0
server
cloudflare
vary
Accept-Encoding
GET
H2
200
icon-totomacau5d.jpg
qqtotokiwi.site/assets/img/icon/
9 KB
9 KB
88ms
46ms
Image
image/jpeg
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/img/icon/icon-totomacau5d.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
157c3fc50a9a79068835c64a4a57ad51f33cebff9c177e171e632d1e99134b84

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cache-control
public, max-age=2592000
cf-cache-status
MISS
etag
"66028b10-22b9"
cf-ray
961cfe2e3d823e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
8889
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
image/jpeg
last-modified
Tue, 26 Mar 2024 08:45:04 GMT
x-cache-hits
0
server
cloudflare
vary
Accept-Encoding
GET
H2
200
icon-24d.jpg
qqtotokiwi.site/assets/img/icon/
6 KB
6 KB
93ms
52ms
Image
image/jpeg
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/img/icon/icon-24d.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
df5bfec8fd98e9195fb9f02960c1f2a06deb9f024dd04801a45b772feffbf5dd

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cache-control
public, max-age=2592000
cf-cache-status
MISS
etag
"650bd9bd-161e"
cf-ray
961cfe2e3d833e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
5662
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
image/jpeg
last-modified
Thu, 21 Sep 2023 05:50:53 GMT
x-cache-hits
0
server
cloudflare
vary
Accept-Encoding
GET
H2
200
icon-roulette.jpg
qqtotokiwi.site/assets/img/icon/
6 KB
6 KB
96ms
55ms
Image
image/jpeg
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/img/icon/icon-roulette.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
df04e5456a26d89d36120c6078dadfb6e84b37b635c5b8f75a1ac75c27e1fc41

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cache-control
public, max-age=2592000
cf-cache-status
MISS
etag
"66028b10-1749"
cf-ray
961cfe2e3d843e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
5961
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
image/jpeg
last-modified
Tue, 26 Mar 2024 08:45:04 GMT
x-cache-hits
0
server
cloudflare
vary
Accept-Encoding
GET
H2
200
icon-sicbo[dice].jpg
qqtotokiwi.site/assets/img/icon/
6 KB
6 KB
89ms
48ms
Image
image/jpeg
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/img/icon/icon-sicbo[dice].jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
944e25293de1902e94503301ab274b4348c7d48828414eee613fdbfc614dd74c

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cache-control
public, max-age=2592000
cf-cache-status
MISS
etag
"66028b10-18fd"
cf-ray
961cfe2e3d853e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
6397
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
image/jpeg
last-modified
Tue, 26 Mar 2024 08:45:04 GMT
x-cache-hits
0
server
cloudflare
vary
Accept-Encoding
GET
H2
200
icon-sydney.jpg
qqtotokiwi.site/assets/img/icon/
4 KB
5 KB
92ms
52ms
Image
image/jpeg
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/img/icon/icon-sydney.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
e7f471995cff2d274f80d9c96d3d4a066d8731fcea2d52446a93d88bd5e0d878

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cache-control
public, max-age=2592000
cf-cache-status
MISS
etag
"650bd9bd-11b5"
cf-ray
961cfe2e3d863e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
4533
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
image/jpeg
last-modified
Thu, 21 Sep 2023 05:50:53 GMT
x-cache-hits
0
server
cloudflare
vary
Accept-Encoding
GET
H2
200
bca.png
qqtotokiwi.site/assets/img/global/banks/
1 KB
1 KB
87ms
47ms
Image
image/png
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/img/global/banks/bca.png?v=1752957196
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
b60a19eb59f86325af0f4c3e4736e6ed7f3ecc1cadd6efe316e90ae7a75f0ce7

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cache-control
public, max-age=2592000
cf-cache-status
MISS
etag
"670cafe0-43e"
cf-ray
961cfe2e3d873e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
1086
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
image/png
last-modified
Mon, 14 Oct 2024 05:45:04 GMT
x-cache-hits
0
server
cloudflare
vary
Accept-Encoding
GET
H2
200
bni.png
qqtotokiwi.site/assets/img/global/banks/
1 KB
1 KB
84ms
45ms
Image
image/png
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/img/global/banks/bni.png?v=1752957196
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
50afebd206f7b1ef8fcf1d4dff496412a08518bc068319f97465908441cd4041

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cache-control
public, max-age=2592000
cf-cache-status
MISS
etag
"670cafe0-4da"
cf-ray
961cfe2e3d883e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
1242
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
image/png
last-modified
Mon, 14 Oct 2024 05:45:04 GMT
x-cache-hits
0
server
cloudflare
vary
Accept-Encoding
GET
H2
200
bri.png
qqtotokiwi.site/assets/img/global/banks/
1 KB
1 KB
92ms
53ms
Image
image/png
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/img/global/banks/bri.png?v=1752957196
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
5cac9c4ea7470f69937f3e0c66643af243f022ba1d0d1b92ea0b891be8d3e708

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cache-control
public, max-age=2592000
cf-cache-status
MISS
etag
"670cafe0-410"
cf-ray
961cfe2e3d8a3e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
1040
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
image/png
last-modified
Mon, 14 Oct 2024 05:45:04 GMT
x-cache-hits
0
server
cloudflare
vary
Accept-Encoding
GET
H2
200
dana.png
qqtotokiwi.site/assets/img/global/banks/
2 KB
2 KB
89ms
50ms
Image
image/png
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/img/global/banks/dana.png?v=1752957196
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
eb6f10f5452fd08234a524d21df41a6b9be1466c0c3acd39017951cd4122a3cf

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cache-control
public, max-age=2592000
cf-cache-status
MISS
etag
"670cafe0-8b9"
cf-ray
961cfe2e3d8b3e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
2233
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
image/png
last-modified
Mon, 14 Oct 2024 05:45:04 GMT
x-cache-hits
0
server
cloudflare
vary
Accept-Encoding
GET
H2
200
gopay.png
qqtotokiwi.site/assets/img/global/banks/
4 KB
4 KB
95ms
57ms
Image
image/png
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/img/global/banks/gopay.png?v=1752957196
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
c1e6c3f3fa6029282b8d718f2088fd4dfd5ea272fcb63bc37f95e66df9918df2

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cache-control
public, max-age=2592000
cf-cache-status
MISS
etag
"670cafe0-fce"
cf-ray
961cfe2e3d8c3e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
4046
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
image/png
last-modified
Mon, 14 Oct 2024 05:45:04 GMT
x-cache-hits
0
server
cloudflare
vary
Accept-Encoding
GET
H2
200
mandiri.png
qqtotokiwi.site/assets/img/global/banks/
1 KB
1 KB
99ms
62ms
Image
image/png
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/img/global/banks/mandiri.png?v=1752957196
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
5e829a18cd9f27940b0bcfd8cbdc4395f368de18d89fd96bf09fcd5cf267a58a

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cache-control
public, max-age=2592000
cf-cache-status
MISS
etag
"670cafe0-467"
cf-ray
961cfe2e3d8d3e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
1127
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
image/png
last-modified
Mon, 14 Oct 2024 05:45:04 GMT
x-cache-hits
0
server
cloudflare
vary
Accept-Encoding
GET
H2
200
ovo.png
qqtotokiwi.site/assets/img/global/banks/
4 KB
5 KB
91ms
54ms
Image
image/png
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/img/global/banks/ovo.png?v=1752957196
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
71dfe3342d07e446916111fed9de1724bdde56c963c1b2573b7ec643e9f26e50

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cache-control
public, max-age=2592000
cf-cache-status
MISS
etag
"670cafe0-11e2"
cf-ray
961cfe2e3d8f3e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
4578
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
image/png
last-modified
Mon, 14 Oct 2024 05:45:04 GMT
x-cache-hits
0
server
cloudflare
vary
Accept-Encoding
GET
H2
200
qqbank.png
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgaN0RMgNArFEgUv1AuYb5ftQrAsaDmUEi6JN6ec3uvpIhWl0zDuqeLbFcP9ls7FycjUMp2WVCtjwL2aMAyiqroEryxuKzuzWqPiyJpTD6gG3gxlluRQftyt7lSZEXqYx2J6uvwUwF0i_Lj-Q7W...
148 KB
148 KB
1113ms
1077ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgaN0RMgNArFEgUv1AuYb5ftQrAsaDmUEi6JN6ec3uvpIhWl0zDuqeLbFcP9ls7FycjUMp2WVCtjwL2aMAyiqroEryxuKzuzWqPiyJpTD6gG3gxlluRQftyt7lSZEXqYx2J6uvwUwF0i_Lj-Q7WCfhwtNlOmMANL6eQXLS24rKtNoY7oNOMJgED4EkmVWc/s16000/qqbank.png
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
f6a9278652be2fb55f6dd5aa3af7b522a0a10dcc8aef682a40ba2bf461b41bdc
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v88"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
151120
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="qqbank.png"
GET
H2
200
qqtoto.png
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjq7nd9Dy6MRrxhgMz6Dsl9Oxs2SAd1eCes1a7unlNIFyu5O-WUsvCzwO4TvCPQ39DW3-mGvjBVWlxVH5vKDbzikDy4tTKbCbJ4g_x15XI-vQS1UQU1Qd8NkEoySEysFlvtGZxpDObvxhu5wF2T...
134 KB
134 KB
1146ms
1112ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjq7nd9Dy6MRrxhgMz6Dsl9Oxs2SAd1eCes1a7unlNIFyu5O-WUsvCzwO4TvCPQ39DW3-mGvjBVWlxVH5vKDbzikDy4tTKbCbJ4g_x15XI-vQS1UQU1Qd8NkEoySEysFlvtGZxpDObvxhu5wF2T563wXxDf-dn0L_qSB8EhWvxZjfgX0281jXqTLkyqr-U/s16000/qqtoto.png
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
94e8ab01225044ea5cee0572773045dc3193583f730ba68df0b551bef0d88515
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v88"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
137219
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="qqtoto.png"
GET
H2
200
SLOT-GAMES-TEXT-BUTTON.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiThZqjo0ONlKc5enL9hV1Vbm2Is4PmYQiuy3dlowAgEewQ3Bsa8YjJY4Nqz5oJvuCd-hP1o78eya0bTanbcYy3ZiSNuZSaHCOOkZTvZqqdSD6HTxKDAE2wHB7xPM2tYRsb_sw3sNwFsQblzmhK...
15 KB
16 KB
1033ms
1000ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiThZqjo0ONlKc5enL9hV1Vbm2Is4PmYQiuy3dlowAgEewQ3Bsa8YjJY4Nqz5oJvuCd-hP1o78eya0bTanbcYy3ZiSNuZSaHCOOkZTvZqqdSD6HTxKDAE2wHB7xPM2tYRsb_sw3sNwFsQblzmhKzbkGboQegDkspA37jm12wcEyavvHIIBAhcvO2z5cUgo/s16000/SLOT-GAMES-TEXT-BUTTON.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
f807e579e83fd6daa687a9d7e0a919a8e7300d1a662df012cf5cedd5c8049641
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v51"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
15764
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="SLOT-GAMES-TEXT-BUTTON.gif"
GET
H2
200
SLOT%20QQ1.webp
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEioLMnlSUhhCpXo-KFSBrUEhlcFETppa8Tk4zNU13G5e6n6Jr-YQf97kaRDJiDTJ1NbzO9wswB7yOnWNzx3dBy50U0YFuO1xUNPrSM5rfhQd3pOSKOauwxBRKWJhlZ3V081YVru08XTQ_mxaDnU...
192 KB
192 KB
1139ms
1107ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEioLMnlSUhhCpXo-KFSBrUEhlcFETppa8Tk4zNU13G5e6n6Jr-YQf97kaRDJiDTJ1NbzO9wswB7yOnWNzx3dBy50U0YFuO1xUNPrSM5rfhQd3pOSKOauwxBRKWJhlZ3V081YVru08XTQ_mxaDnUaz-Vps2UFh5eQwrzl65OHB3bpo-ovJN-Ag7En1XP8bo/s16000/SLOT%20QQ1.webp
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
acc0849cb6eb4d29e53f9002dbecee197245e94232cf6dd2eb7342c452d6e40f
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v51"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
196119
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="SLOT QQ1.png"
GET
H2
200
SLOT%20QQ2.webp
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiBBEiw-mRZ9js650RtboAcxa0g2TwauSnEWr2-3LqohRgM32yHNpNoNY5sLrXdRwd5edt1AAYzNCyWDo3UXY7BZUo6h6Bzxx_KtxiqxHbhGdz1EMwErBQMs2z6SnbqpL8S1cCmt811xjeHPLWO...
184 KB
185 KB
860ms
828ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiBBEiw-mRZ9js650RtboAcxa0g2TwauSnEWr2-3LqohRgM32yHNpNoNY5sLrXdRwd5edt1AAYzNCyWDo3UXY7BZUo6h6Bzxx_KtxiqxHbhGdz1EMwErBQMs2z6SnbqpL8S1cCmt811xjeHPLWODYMAg33TUyMQSvH1pcKTAwx5oJk6uTPr9rAwXuWxWhg/s16000/SLOT%20QQ2.webp
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
9881bc01e3ea57d351587a346c64a63729f1bd7e9d63e4e1345e9ccc2158c85a
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v51"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
188912
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="SLOT QQ2.png"
GET
H2
200
SLOT%20QQ3.webp
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEirpVWIBYpbbap64Jbo-FInHvKz3XvLOPLtykEcAFiFlTlkQ3ZijFQ-Jj17Z11tVWrByvKrV1_q0insp9bcP4j5jsOgy2ZSHKPWfMKZ1CgxoUda4zRMGkrK0eMliARjpIzyLTNQv3ZNa7keua5O...
181 KB
181 KB
995ms
964ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEirpVWIBYpbbap64Jbo-FInHvKz3XvLOPLtykEcAFiFlTlkQ3ZijFQ-Jj17Z11tVWrByvKrV1_q0insp9bcP4j5jsOgy2ZSHKPWfMKZ1CgxoUda4zRMGkrK0eMliARjpIzyLTNQv3ZNa7keua5OV7rB_RUm_C9t40XXnEga78pAOvkI2iR-1AssrGE8Bzc/s16000/SLOT%20QQ3.webp
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
fac2cd7d30dfe3162bda5a424d32221b801dec5a627cdd7bffcd03ba67e6928f
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v51"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
185429
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="SLOT QQ3.png"
GET
H2
200
SLOT%20QQ5.webp
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjRuzWHP5bKmafPC4eg7wl5e1rifoPCH-E8i6BcO_buTvkq1RimjyomZykoziCv4Ao2zik9fzPnfpo1qHFlNTXZITG9LiwC3e2aH9WqRTblzkNj5y7L3xJXFB4whzarc6AICvTm0j_xqn6saC28...
172 KB
172 KB
1253ms
1222ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjRuzWHP5bKmafPC4eg7wl5e1rifoPCH-E8i6BcO_buTvkq1RimjyomZykoziCv4Ao2zik9fzPnfpo1qHFlNTXZITG9LiwC3e2aH9WqRTblzkNj5y7L3xJXFB4whzarc6AICvTm0j_xqn6saC28rqLmoOLkzhT5-fU-VgLLcsaLP9BVlNWMgL21PMF1IPw/s16000/SLOT%20QQ5.webp
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
0a0ebaa25971f58c3366e5c50f4a3b843a758239c718fbb16190f117364d1bdd
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v51"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
175777
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="SLOT QQ5.png"
GET
H2
200
SLOT%20QQ6.webp
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjr8NdY7CSk8MnKFmjn2dnQLExp1OUIL4b91jodUL2-nmx_ncZqW0TrPVxyIH-Wvw8OkPYRl8sBUc1XbffVhXQYPDYBAW2YAZmMRqK2oYws2FLwSJdoxB4GifPToOMAU5mNBKmRx8MCeGl9LUxa...
143 KB
143 KB
1087ms
1057ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjr8NdY7CSk8MnKFmjn2dnQLExp1OUIL4b91jodUL2-nmx_ncZqW0TrPVxyIH-Wvw8OkPYRl8sBUc1XbffVhXQYPDYBAW2YAZmMRqK2oYws2FLwSJdoxB4GifPToOMAU5mNBKmRx8MCeGl9LUxaZsilYxrAcC0PyWxO4g_hy1bDKyg2PjYLGDrwqG7Viqg/s16000/SLOT%20QQ6.webp
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
97e599f952ceae0ee2e64cf0f3484b8d08c7db8e7f959effa33b19b8584b48cf
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v51"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
146155
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="SLOT QQ6.png"
GET
H2
200
SLOT%20QQ7.webp
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEh8j-cJmFdgV72hBIhMrT_LNzgru_qE4fBAKapdXKb99s-W7ERRshbCN9lJifMZXydycslgYPdJk5GN-30u_mUV0a3_u3vn-8myUaGGLMQib6ZXv1xue7u8lUmQ6kSFMC4owMIHQwcYCFmbZTBm...
152 KB
152 KB
1115ms
1085ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEh8j-cJmFdgV72hBIhMrT_LNzgru_qE4fBAKapdXKb99s-W7ERRshbCN9lJifMZXydycslgYPdJk5GN-30u_mUV0a3_u3vn-8myUaGGLMQib6ZXv1xue7u8lUmQ6kSFMC4owMIHQwcYCFmbZTBmmSZyjg79IgLF7h0CQr-gC8F5XazojkmTu3G2vq_dFwI/s16000/SLOT%20QQ7.webp
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
7ebacae5f7c966d5958232cfb7b6caec90e5f5163b80914ef8661c3cd342ad5b
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v51"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
155773
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="SLOT QQ7.png"
GET
H2
200
SLOT%20QQ8.webp
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEg2-YNGll_WeWPynxvctFLI66AF__C0oNs4HUR2DjvFcWNAMcAT8DIo-r5sRnnuJZy24reZvj4S6bIbX2YBAxM2gZUJLpReb5fjWAkHR7bJYMd5e65bBUdWTbROzWhZFziVsYQGokqSdPIb07ZZ...
180 KB
180 KB
1120ms
1092ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEg2-YNGll_WeWPynxvctFLI66AF__C0oNs4HUR2DjvFcWNAMcAT8DIo-r5sRnnuJZy24reZvj4S6bIbX2YBAxM2gZUJLpReb5fjWAkHR7bJYMd5e65bBUdWTbROzWhZFziVsYQGokqSdPIb07ZZtdTTxrhxZaLuYtd2Cgysd1pGThO5GVEVL5lCCM0cvVA/s16000/SLOT%20QQ8.webp
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
dc6ad4aa6efe488b3c2cc362183d8a2420dc87e484587cacc46dceac4a6b84f4
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v51"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
184004
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="SLOT QQ8.png"
GET
H2
200
SLOT%20QQ4.webp
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhqfCx1ZVWveAGtGvstnTKLSq36WILSFswlrtrpQBc7w-PA22IoybpWK3GlkuW-Z0Dq5QCGG_ORFj5Ebt7fxrdG2ewJJM97BZjViBJCYv9tQIhYwR_PrZecpg4Wm9_7r_pzRKtAJfscGXpqaNT2...
174 KB
174 KB
1182ms
1154ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhqfCx1ZVWveAGtGvstnTKLSq36WILSFswlrtrpQBc7w-PA22IoybpWK3GlkuW-Z0Dq5QCGG_ORFj5Ebt7fxrdG2ewJJM97BZjViBJCYv9tQIhYwR_PrZecpg4Wm9_7r_pzRKtAJfscGXpqaNT2j8tSDNuPDGDSI52Qb-ZcU4n07w_2uzOusX0abjZQwd8/s16000/SLOT%20QQ4.webp
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
23d2b335b6210ff91d9d438cad7f2301456f0e006384ef95f353f120dc374586
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v51"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
178420
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="SLOT QQ4.png"
GET
H2
200
casino-TEXT-BUTTON.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhGVUu2rbQBNeBgHaPXl3-eW1_7fGAR0C9IzMlngo-zQZUjN5NDKlXsk-H_VxaZg23Q34l3tr2KMu-DGDvAmhVswHPXQJdZ3H25Iesxbb2CnMklNz4JUde9r7V23IWL82Ogd4IjcIAfnAo-itPd...
17 KB
17 KB
1193ms
1166ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhGVUu2rbQBNeBgHaPXl3-eW1_7fGAR0C9IzMlngo-zQZUjN5NDKlXsk-H_VxaZg23Q34l3tr2KMu-DGDvAmhVswHPXQJdZ3H25Iesxbb2CnMklNz4JUde9r7V23IWL82Ogd4IjcIAfnAo-itPdUxVYNH9KMawUPqDoXrcgrw7hHCcu_XL93CwpN9EvJg4/s16000/casino-TEXT-BUTTON.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
229c5efa60567b67d2b8513a5c5944c75270b0f6f32f394ba9a540a5a5de4870
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v72"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
17299
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="casino-TEXT-BUTTON.gif"
GET
H2
200
CASINO%20QQ1.webp
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEj-Eo2z3i4tAOKabgTjHpXgupToQ4DdSD2ObGKco_CZs4vStXBHQMkkT0f1oTP6ZaN9-A3Nu9JJgYueYPjMxwJiv11tcnops1WXKqmGRZrFXQd6GXM0TYJyndrnF4thngbxqzyjKrJ5rMI2COUV...
176 KB
176 KB
1095ms
1068ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEj-Eo2z3i4tAOKabgTjHpXgupToQ4DdSD2ObGKco_CZs4vStXBHQMkkT0f1oTP6ZaN9-A3Nu9JJgYueYPjMxwJiv11tcnops1WXKqmGRZrFXQd6GXM0TYJyndrnF4thngbxqzyjKrJ5rMI2COUVr5aBAJ8bCa-rRQDWVokNhA03IoyQYQpp4odoJUCt6SU/s16000/CASINO%20QQ1.webp
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
6eaa0b875e0b645445f4e6d54c92397c90f2124cd8f2e5c66c34b18a4b1e1d0f
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v72"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
180377
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="CASINO QQ1.png"
GET
H2
200
CASINO%20QQ2.webp
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEg2segL8hWJDd7NRbUvSA0S0Jbrex0LnLX_FuQGwekoqJl-rAz-2lh7BffPvMUpI8B3p1LPjgSPYVAeBmsVZrOjM8mxRSgNkcbrcCJepH461CMX_uEzqG7kdasLG3tCKdc3jWRhbFIo6tZB3MXm...
168 KB
168 KB
1242ms
1216ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEg2segL8hWJDd7NRbUvSA0S0Jbrex0LnLX_FuQGwekoqJl-rAz-2lh7BffPvMUpI8B3p1LPjgSPYVAeBmsVZrOjM8mxRSgNkcbrcCJepH461CMX_uEzqG7kdasLG3tCKdc3jWRhbFIo6tZB3MXmuBI2h-y0FjRxYp6X1-Lyl2br-gu3-3568-pL09R_35Q/s16000/CASINO%20QQ2.webp
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
a9aae7f8a5dd0abfc486c0f4027795598ab0330d297e515376333d24e78385f8
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v72"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
171850
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="CASINO QQ2.png"
GET
H2
200
CASINO%20QQ3.webp
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEh-OV8YUeYFRTL7GABlSFwXWfHopwPi6sKmZQ0kxlDNDWriKSQFUnTU7epyiyASiNkNFtYO41rhZLtwUoYHIVSsha4GX8ZPww1Pawu7l83Cqu1NfG7TZxqs1Rk_SmX9dACewmGEHq9bvd8S_1It...
189 KB
189 KB
936ms
911ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEh-OV8YUeYFRTL7GABlSFwXWfHopwPi6sKmZQ0kxlDNDWriKSQFUnTU7epyiyASiNkNFtYO41rhZLtwUoYHIVSsha4GX8ZPww1Pawu7l83Cqu1NfG7TZxqs1Rk_SmX9dACewmGEHq9bvd8S_1ItLOg07xnlemGFZexfWnLwgiHtOGqJZ4ERT9xo-LeJJ2U/s16000/CASINO%20QQ3.webp
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
19afcb54d051bc5f6897ca91dc7c92b0ff1993f03379f0a7b2182edbb672ba68
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v72"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
193432
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="CASINO QQ3.png"
GET
H2
200
CASINO%20QQ4.webp
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgillTttlT1pLbsu1lI9wgHQWeyhtaUlLpPct0uuqcwgGJcOBWeyAHjKuwwqcNbTfi21lqtUwFPqyolTp5lJylGPmJ_QKL4kECahKhtfe89vYfkSp5sqCPcxsXNMJReabw1j0hXd6yLRWN0uaYZ...
165 KB
165 KB
1157ms
1134ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgillTttlT1pLbsu1lI9wgHQWeyhtaUlLpPct0uuqcwgGJcOBWeyAHjKuwwqcNbTfi21lqtUwFPqyolTp5lJylGPmJ_QKL4kECahKhtfe89vYfkSp5sqCPcxsXNMJReabw1j0hXd6yLRWN0uaYZTuwCTHzZWjWm-PGdRNn3sh6HLc_52slwV2wF5QzoFnE/s16000/CASINO%20QQ4.webp
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
cf6071b1e482ced4345fe12749d8cd348290e03bcdc1baeb8792f81979355b00
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v72"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
169249
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="CASINO QQ4.png"
GET
H2
200
CASINO%20QQ5.webp
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjRaqageYCga0z0uoTfyAVi2-YXjtakRSNUmwBIoB3z2QahTWwzx1PksUnFCZHy12uGvZ8_src2v6N4DTQ8EPHa3-3zS5YpPldS1_f2_pTI9vb5_tgLYZ8tm2D_envnvyS_qGGKROoMVHRK85bR...
181 KB
181 KB
933ms
910ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjRaqageYCga0z0uoTfyAVi2-YXjtakRSNUmwBIoB3z2QahTWwzx1PksUnFCZHy12uGvZ8_src2v6N4DTQ8EPHa3-3zS5YpPldS1_f2_pTI9vb5_tgLYZ8tm2D_envnvyS_qGGKROoMVHRK85bRi3J2Jo2uedkzk7ogsT9ynnQvgQEel_BuwyGXsFImmlE/s16000/CASINO%20QQ5.webp
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
d7a54fdb553b91383f1d6f043d10573d88dd023370e76f27e86544dfacf9ce46
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v72"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
185543
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="CASINO QQ5.png"
GET
H2
200
CASINO%20QQ6.webp
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiXRJ3GPJVUCs2FcP7E_vh1W6nXgDnlaW9vMv2IVC87Os8O0FGN-EXIZ8mQ9rB8dXWqBAp82yaFZROEMyNMecf2HgeYBG1h0a07gyoR5hdfMU__qKp3vG-8D2W4_LcmuIqWJS1zac-MP7KfVi13...
182 KB
182 KB
1104ms
1081ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiXRJ3GPJVUCs2FcP7E_vh1W6nXgDnlaW9vMv2IVC87Os8O0FGN-EXIZ8mQ9rB8dXWqBAp82yaFZROEMyNMecf2HgeYBG1h0a07gyoR5hdfMU__qKp3vG-8D2W4_LcmuIqWJS1zac-MP7KfVi13vjmnLzTxU3A_rr50tgOXgWQrbI49FYZXQHaZ3_ok5zw/s16000/CASINO%20QQ6.webp
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
2c4f35c70137a8754b6a2ff493e9acf449c05c8197fa76d80cc66a897aef4d88
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v72"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
185945
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="CASINO QQ6.png"
GET
H2
200
CASINO%20QQ7.webp
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhACVXFWyeP_GV38qGEmItVnOdk5JcSnQgGNNfHOy6SxEVR4lYCxDDMIrY7cUixiKsdxj8Vl95AiFBs9mqeF0EUJ5wXPRBUzxNLZJfVo5mNrScs2eWkAitHnHhTbicZogRrL5xOy1wemNmN5JoU...
175 KB
175 KB
1208ms
1186ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhACVXFWyeP_GV38qGEmItVnOdk5JcSnQgGNNfHOy6SxEVR4lYCxDDMIrY7cUixiKsdxj8Vl95AiFBs9mqeF0EUJ5wXPRBUzxNLZJfVo5mNrScs2eWkAitHnHhTbicZogRrL5xOy1wemNmN5JoUuFYy4p26dc6aOrFxfys8RHkWBwXfU6XcQpOsldE8hyphenhyphenw/s16000/CASINO%20QQ7.webp
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
c24b18ffc29b98248f2c02397ce2ef0c777d7d4f2ca18800154e39d021a6010f
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v72"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
179083
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="CASINO QQ7.png"
GET
H2
200
CASINO%20QQ8.webp
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjCysO6t59oVa1f_iIZYWBBVn8d1qiEnqo_WKP0Wy0MeLa8vIptdWM4MAxCqNH-IvzUQUPX4LmxWOw9wvZadQHxzlIJziWEpLe8_N0HDjwiZL40ZCw00vR4zm_JvOS83hCCOBIqpnEPHuEp5Q0i...
181 KB
181 KB
1291ms
1269ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjCysO6t59oVa1f_iIZYWBBVn8d1qiEnqo_WKP0Wy0MeLa8vIptdWM4MAxCqNH-IvzUQUPX4LmxWOw9wvZadQHxzlIJziWEpLe8_N0HDjwiZL40ZCw00vR4zm_JvOS83hCCOBIqpnEPHuEp5Q0iDhy0cF_ripPTjpsemBVbFVmD34qrcbFwno7jCKrEH88/s16000/CASINO%20QQ8.webp
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
cbdd8b7572a4b646b8e016a55904309399dddf483be439380e8997106bac0786
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v72"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
185611
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="CASINO QQ8.png"
GET
H2
200
link-TEXT-BUTTON.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgKK8N4KQ32klGICgxO2-zg17IBTFtvThW-MLAgB-us1ZzNBwoWJC9Vh01XgSgaJ5MVF50LSyo8PjJPERXe03Q_SRpr_BO-JtPH2BfQdPIg2x2sLREul5I3dKy9n_ZzblLoiJxGehhYTqYoETb-...
16 KB
17 KB
1021ms
999ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgKK8N4KQ32klGICgxO2-zg17IBTFtvThW-MLAgB-us1ZzNBwoWJC9Vh01XgSgaJ5MVF50LSyo8PjJPERXe03Q_SRpr_BO-JtPH2BfQdPIg2x2sLREul5I3dKy9n_ZzblLoiJxGehhYTqYoETb-_Wouh85Tm6vZEbmQl40zd37MUKsXWu4CNzNWc8XN_u8/s16000/link-TEXT-BUTTON.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
09b2dd7108d5be7504d9cceeb879e15d7038d60290ba856169d399efb469c1b3
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v77"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
16790
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="link-TEXT-BUTTON.gif"
GET
H2
200
QQTOTO%20GAME.webp
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiuJMdPXl0r7BwmcCy1680wpSDSJwf_IE_sBr5Ua_iagWQlo32jdF9Pg9ou9v_GWRpY7UfuUKp4DvyN8xgoEI4OLXCqhkHH3dCZHinVDS2TkkrWZFlXMJdo2fepxL1u44aZ2tS8nWKU0Jya-etj...
153 KB
153 KB
940ms
920ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiuJMdPXl0r7BwmcCy1680wpSDSJwf_IE_sBr5Ua_iagWQlo32jdF9Pg9ou9v_GWRpY7UfuUKp4DvyN8xgoEI4OLXCqhkHH3dCZHinVDS2TkkrWZFlXMJdo2fepxL1u44aZ2tS8nWKU0Jya-etjvLPS3_JPECpgtMa968cyyk9_oPD59oG3ECJst_M9mjU/s16000/QQTOTO%20GAME.webp
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
fc7764b77d15e6e8d319bbceea046fc891f84213e23f4014c7df21d541bd53f8
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v88"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
156848
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="QQTOTO GAME.png"
GET
H2
200
797917448_1920%20x%20154.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEipPR0Xc9QsxbNN1ejyWcpEl98N9A1yqzMkkblvnXbXnU9iaK1AsLL1fVLiiNFU2cB6dSpl7enD1L-gkYDmLmja-B546LOOTfNpOd_lsvov7C40YpyKjr73Hb2WGY5R_Tdayak70Eu80aSW-xTe...
350 KB
350 KB
1160ms
1140ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEipPR0Xc9QsxbNN1ejyWcpEl98N9A1yqzMkkblvnXbXnU9iaK1AsLL1fVLiiNFU2cB6dSpl7enD1L-gkYDmLmja-B546LOOTfNpOd_lsvov7C40YpyKjr73Hb2WGY5R_Tdayak70Eu80aSW-xTebHrKNfbbfyH0S46PYIwAsruUBnzd3I2TB_sHc_SU4Ec/s16000/797917448_1920%20x%20154.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
e73672b9ee5ccfb007c410d8b9d4455e2514a7d7cb2dcf971572dc289bbb9c5b
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v88"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
358498
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="797917448_1920 x 154.gif"
GET
H2
200
modernizr-2.6.2-respond-1.1.0.min.js Show response
qqtotokiwi.site/assets/js/vendor/
18 KB
7 KB
75ms
17ms
Script
application/javascript
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/js/vendor/modernizr-2.6.2-respond-1.1.0.min.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
bf2d2ce2803063fd72be8165d5fbbc700e24dfd6bfcb351f064367a90db9ef4e

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"6466f3b1-4812"
cf-ray
961cfe2e3d683e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
application/javascript
last-modified
Fri, 19 May 2023 03:57:37 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
bootstrap.min.js Show response
qqtotokiwi.site/assets/js/vendor/bootstrap/
31 KB
8 KB
73ms
16ms
Script
application/javascript
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/js/vendor/bootstrap/bootstrap.min.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
8ae9a41def07afb4166b08e3143071437d1867e5f26e6bd907899a8b50bbafbb

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"6466f3b1-7ba2"
cf-ray
961cfe2e3d693e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
application/javascript
last-modified
Fri, 19 May 2023 03:57:37 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
skrollr.min.js Show response
qqtotokiwi.site/assets/js/vendor/skrollr/
12 KB
5 KB
74ms
16ms
Script
application/javascript
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/js/vendor/skrollr/skrollr.min.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
911dccc7a59863b46d628fdac57d96a7cbf72325fe2555d2a3d165c6258d3464

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"6466f3b1-3048"
cf-ray
961cfe2e3d6b3e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
5418
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
application/javascript
last-modified
Fri, 19 May 2023 03:57:37 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
jquery.simple-text-rotator.js Show response
qqtotokiwi.site/assets/js/vendor/text-rotator/
3 KB
855 B
76ms
19ms
Script
application/javascript
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/js/vendor/text-rotator/jquery.simple-text-rotator.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
95df7f4d192968c5c68e43a936016ad025fac7ce02a221a1bf13be6592667c30

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"6466f3b1-df0"
cf-ray
961cfe2e3d6c3e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
application/javascript
last-modified
Fri, 19 May 2023 03:57:37 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
owl.carousel.min.js Show response
qqtotokiwi.site/assets/js/vendor/owl-carousel/
15 KB
7 KB
75ms
18ms
Script
application/javascript
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/js/vendor/owl-carousel/owl.carousel.min.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
4b18105a346260a3e8359cd02633fd5f8bb244f2d5f43e4375a1efd10e5c865a

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"6466f3b1-3a44"
cf-ray
961cfe2e3d6d3e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
application/javascript
last-modified
Fri, 19 May 2023 03:57:37 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
nivo-lightbox.min.js Show response
qqtotokiwi.site/assets/js/vendor/nivo-lightbox/
7 KB
2 KB
74ms
18ms
Script
application/javascript
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/js/vendor/nivo-lightbox/nivo-lightbox.min.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
65723a3f6bf46e95bd82bbbc3f986c0df44ad1b4427abbc3fa252a53ff40b4ea

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"6466f3b1-1cfc"
cf-ray
961cfe2e3d6f3e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
2090
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
application/javascript
last-modified
Fri, 19 May 2023 03:57:37 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
jquery.tweet.min.js Show response
qqtotokiwi.site/assets/js/vendor/tweet-js/
8 KB
3 KB
79ms
23ms
Script
application/javascript
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/js/vendor/tweet-js/jquery.tweet.min.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
431cff4d223f3296f7d4b543573271745a91d9069a3666844fb3b037aad844c7

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"6466f3b1-2011"
cf-ray
961cfe2e3d703e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
application/javascript
last-modified
Fri, 19 May 2023 03:57:37 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
jflickrfeed.min.js Show response
qqtotokiwi.site/assets/js/vendor/jflickrfeed/
1 KB
754 B
116ms
60ms
Script
application/javascript
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/js/vendor/jflickrfeed/jflickrfeed.min.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
796951855984fed308feec350d31ea2ac1382b2c6aec06412f9c33e1c13fe075

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"6466f3b1-5b6"
cf-ray
961cfe2e3d723e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
650
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
application/javascript
last-modified
Fri, 19 May 2023 03:57:37 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
jquery.appear.js Show response
qqtotokiwi.site/assets/js/vendor/appear/
2 KB
767 B
115ms
59ms
Script
application/javascript
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/js/vendor/appear/jquery.appear.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
5d19547b40e94ab90e831bec03fc23d4b894894bb93006b3b3fd8d62e2f355ca

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"6466f3b1-610"
cf-ray
961cfe2e3d733e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
application/javascript
last-modified
Fri, 19 May 2023 03:57:37 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
jquery.parallax-1.1.3.js Show response
qqtotokiwi.site/assets/js/vendor/parallax/
941 B
507 B
107ms
51ms
Script
application/javascript
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/js/vendor/parallax/jquery.parallax-1.1.3.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
ba75543913b3258b7a19cdea608c7cc47322898d244b40b6190c970be2d3a2fd

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"6466f3b1-3ad"
cf-ray
961cfe2e3d743e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
application/javascript
last-modified
Fri, 19 May 2023 03:57:37 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
jquery.li-scroller.1.0.js Show response
qqtotokiwi.site/assets/js/vendor/liScroller/
1002 B
515 B
75ms
19ms
Script
application/javascript
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/js/vendor/liScroller/jquery.li-scroller.1.0.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
e00749ed99da6de8ee85c1fa969a7571feaba5a506c1dd88be8a12e20ed680d9

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"6466f3b1-3ea"
cf-ray
961cfe2e3d753e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
436
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
application/javascript
last-modified
Fri, 19 May 2023 03:57:37 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
jquery.cycle2.min.js Show response
qqtotokiwi.site/assets/js/
22 KB
7 KB
80ms
24ms
Script
application/javascript
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/js/jquery.cycle2.min.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
6b41e47a54aefc08aaa3678ed56f5689ddf69b8e8a48e9af8acc200ed0559fec

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"6466f3b1-5710"
cf-ray
961cfe2e3d763e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
application/javascript
last-modified
Fri, 19 May 2023 03:57:37 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
jquery.fixedheadertable.min.js Show response
qqtotokiwi.site/assets/js/
10 KB
3 KB
103ms
48ms
Script
application/javascript
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/js/jquery.fixedheadertable.min.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
991994866beb5e90d2205f4c5d4a757ddd38c6399386335991b260a89d857fa1

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"6466f3b1-298b"
cf-ray
961cfe2e3d773e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
3237
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
application/javascript
last-modified
Fri, 19 May 2023 03:57:37 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
style.js Show response
qqtotokiwi.site/assets/js/
6 KB
2 KB
88ms
33ms
Script
application/javascript
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/js/style.js?v=1.0
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
d943adf3ed1dad80fb33a3380e56e5a584293f8d1694dbb6d5c5d1c6036ee406

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"6466f3b1-16de"
cf-ray
961cfe2e3d793e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
2144
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
application/javascript
last-modified
Fri, 19 May 2023 03:57:37 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
login.js Show response
qqtotokiwi.site/js/auth/
32 KB
10 KB
104ms
50ms
Script
application/javascript
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/js/auth/login.js?v=c3syfye1yivoif3u4mel
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
0f06109a3edc4b5015427cb22d029aa91a72acd32b71ce5079818fd6598241a6

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"67fdf112-7fb7"
cf-ray
961cfe2e3d7a3e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
application/javascript
last-modified
Tue, 15 Apr 2025 05:39:30 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
index.js Show response
qqtotokiwi.site/js/frontend/desktop/template_v1/before/
12 KB
4 KB
108ms
54ms
Script
application/javascript
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/js/frontend/desktop/template_v1/before/index.js?v=c3syfye1yivoif3u4mel
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
7f1d23659e76eca87d310351b7598a64201f99a8be2a947319f0182cdc3b0cd2

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"67fdf112-3078"
cf-ray
961cfe2e3d7b3e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
application/javascript
last-modified
Tue, 15 Apr 2025 05:39:30 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
floating_icons.min.js Show response
qqtotokiwi.site/js/custom/
1 KB
752 B
79ms
25ms
Script
application/javascript
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/js/custom/floating_icons.min.js?v=1752957196
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
afbf313c9cd8546932da922fcd36f00f9e0787370ac0d46ca82d3cb31d15d0ea

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"67db872e-494"
cf-ray
961cfe2e3d7c3e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
application/javascript
last-modified
Thu, 20 Mar 2025 03:10:38 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
vcd15cbe7772f49c399c6a5babf22c1241717689176015 Show response
static.cloudflareinsights.com/beacon.min.js/
19 KB
7 KB
133ms
44ms
Script
text/javascript
104.16.79.73
CLOUDFLARENET
General
Full URL
https://static.cloudflareinsights.com/beacon.min.js/vcd15cbe7772f49c399c6a5babf22c1241717689176015
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.16.79.73 , Ascension Island, ASN13335 (CLOUDFLARENET, US),
Reverse DNS
Software
cloudflare /
Resource Hash
8a18d13015336bc184819a5a768447462202ef3105ec511bf42ed8304a7ed94f

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Origin
https://qqtotokiwi.site
Referer
https://qqtotokiwi.site/

Response headers

cache-control
public, max-age=86400
content-encoding
gzip
etag
W/"2024.6.1"
cross-origin-resource-policy
cross-origin
cf-ray
961cfe2ee86dce22-SIN
access-control-allow-origin
*
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
text/javascript;charset=UTF-8
last-modified
Thu, 06 Jun 2024 15:52:56 GMT
vary
Accept-Encoding
server
cloudflare
GET
H2
200
tracking.js Show response
cdn.livechatinc.com/
94 KB
31 KB
125ms
37ms
Script
application/javascript
184.51.6.218
AKAMAI-ASN1 Akama...
General
Full URL
https://cdn.livechatinc.com/tracking.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
184.51.6.218 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a184-51-6-218.deploy.static.akamaitechnologies.com
Software
UploadServer /
Resource Hash
5164805006e9213e6b33a236232a9b89b00b6138944d0486776fae98d16a059e

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

x-goog-metageneration
1
access-control-expose-headers
*
x-goog-hash
crc32c=SpEi6g==, md5=//j4I790zYM/PE8nBnZ+CQ==
content-encoding
br
x-goog-stored-content-encoding
identity
expires
Sun, 20 Jul 2025 04:33:16 GMT
x-goog-stored-content-length
96510
date
Sat, 19 Jul 2025 20:33:16 GMT
last-modified
Wed, 16 Jul 2025 07:36:13 GMT
content-type
application/javascript; charset=utf-8
x-guploader-uploadid
ABgVH89_ZnZJFkWX9O4XDIbL5xzfw0n2qDV--LDSK_MsF677xmpBPmH9cKu9brjLqA4Jxb-C2N7O1wQ
cache-control
public, max-age=28800
x-goog-storage-class
STANDARD
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1752651373574762
content-length
30913
server
UploadServer
GET
H2
200
backqq.png
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgeYoQHQ_kk8ot3gVdHnxhKWa7sdKp9GkSlLhtq6IwP8hdLn07VQ0G4bnq-q8zyYLKVfOzoZqZJccWZtXeHgohLlwZly_z_XVbfsdZIh2E4MIy0DHcwCt4jwoQtgol4IR3C8q2RCugTtzwhigcj...
3 MB
3 MB
1890ms
1872ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgeYoQHQ_kk8ot3gVdHnxhKWa7sdKp9GkSlLhtq6IwP8hdLn07VQ0G4bnq-q8zyYLKVfOzoZqZJccWZtXeHgohLlwZly_z_XVbfsdZIh2E4MIy0DHcwCt4jwoQtgol4IR3C8q2RCugTtzwhigcjAEWKaXpjx_A4mumk_KnMHu3xbIZKlw-WAOALrx79d0s/s16000/backqq.png
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
904f55d535ef456b9d3b9e409ec7a44e302198d3352260914e1691d072ccfc4b
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"va4"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
3154546
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="backqq.png"
GET
H2
200
loader.gif
qqtotokiwi.site/assets/img/
5 KB
5 KB
81ms
63ms
Image
image/gif
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/img/loader.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/assets/css/bsq/bsq2.css
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
a76090f2d604a7e9bd429900001b367ae94f52d749fd0f94706be887d87cce7f

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/assets/css/bsq/bsq2.css

Response headers

cache-control
public, max-age=2592000
cf-cache-status
MISS
etag
"650bd9c1-158d"
cf-ray
961cfe2e5d983e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
5517
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
image/gif
last-modified
Thu, 21 Sep 2023 05:50:57 GMT
x-cache-hits
0
server
cloudflare
vary
Accept-Encoding
GET
H2
200
logo.png
qqtotokiwi.site/assets/img/bsq/
15 KB
15 KB
59ms
57ms
Image
image/png
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/img/bsq/logo.png?v=123
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/assets/css/bsq/bsq2.css
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
8b476f0ed400347d7a4039100a4f8baae69eb909109550177d5a724a3aa8e793

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/assets/css/bsq/bsq2.css

Response headers

cache-control
public, max-age=2592000
cf-cache-status
MISS
etag
"650bd9bb-3ab5"
cf-ray
961cfe2e5d993e06-SIN
expires
Mon, 18 Aug 2025 20:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
15029
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
image/png
last-modified
Thu, 21 Sep 2023 05:50:51 GMT
x-cache-hits
0
server
cloudflare
vary
Accept-Encoding
GET
H2
200
fontawesome-webfont.woff2
qqtotokiwi.site/assets/fonts/
75 KB
76 KB
41ms
41ms
Font
application/octet-stream
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/fonts/fontawesome-webfont.woff2?v=4.7.0
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/assets/css/font-awesome.min.css
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
2adefcbc041e7d18fcf2d417879dc5a09997aa64d675b7a3c4b6ce33da13f3fe

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Origin
https://qqtotokiwi.site
Referer
https://qqtotokiwi.site/assets/css/font-awesome.min.css

Response headers

cache-control
public, max-age=14400
cf-cache-status
MISS
etag
"6466f3ae-12d68"
cf-ray
961cfe2eee013e06-SIN
expires
Sun, 20 Jul 2025 00:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
77160
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
application/octet-stream
last-modified
Fri, 19 May 2023 03:57:34 GMT
x-cache-hits
0
server
cloudflare
vary
Accept-Encoding
GET
H3
200
dazS1PrQQuCxC3iOAJFEJYUt79146ZFaIJxILcpzmhI.woff
fonts.gstatic.com/s/robotoslab/v6/
31 KB
31 KB
29ms
15ms
Font
font/woff
142.251.10.94
GOOGLE
General
Full URL
https://fonts.gstatic.com/s/robotoslab/v6/dazS1PrQQuCxC3iOAJFEJYUt79146ZFaIJxILcpzmhI.woff
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/assets/css/fonts.min.css
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.10.94 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
sd-in-f94.1e100.net
Software
sffe /
Resource Hash
2de6a4f3964c03bb35fb9d54b3de00ac38330f5cd91389a3d462269c27775373
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Origin
https://qqtotokiwi.site
Referer
https://qqtotokiwi.site/

Response headers

age
144058
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Sat, 18 Jul 2026 04:32:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 18 Jul 2025 04:32:18 GMT
last-modified
Thu, 28 Aug 2014 20:40:48 GMT
content-type
font/woff
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
31576
x-xss-protection
0
server
sffe
GET
H2
200
prediksi.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjmqdRqV0K48ktibX-XD0Un6QvlNFdvYL48AO9zCF0pQD5BTbceEnkb7EBqgsFpnUPcSpSXVmW8Mx0FoaM_rCu6mEfYteeIGL2v0U_d8LSu4jMnuTnNR5gPjt_C3BH3ndyCaIZAcWypcV7eZplJ...
1 MB
1 MB
254ms
240ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjmqdRqV0K48ktibX-XD0Un6QvlNFdvYL48AO9zCF0pQD5BTbceEnkb7EBqgsFpnUPcSpSXVmW8Mx0FoaM_rCu6mEfYteeIGL2v0U_d8LSu4jMnuTnNR5gPjt_C3BH3ndyCaIZAcWypcV7eZplJkOvHToPxg5KWMaSv8WWUCV8SeMMlujOfo2mWTg9JA1g/s16000/prediksi.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
598733cd63255150bf43721d0db1234d9512be150fadda472f8ad7876117791b
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v437"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
1159897
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="prediksi.gif"
GET
H2
200
rtp.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjd06y1_jEeKSKgy0bzKtia-EJ90J8F5PxHHj0_QcW6r9SuiHq5pHDt_H6vSJVV-BrEW9eUiN9vaYv-TY4DoPjvpFvWwfCXPIwjDpx4yb0PWs4xnYgWxRbVlPHC9cQOcYTvM5QEbfUVKujy9kdZ...
1 MB
1 MB
496ms
483ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjd06y1_jEeKSKgy0bzKtia-EJ90J8F5PxHHj0_QcW6r9SuiHq5pHDt_H6vSJVV-BrEW9eUiN9vaYv-TY4DoPjvpFvWwfCXPIwjDpx4yb0PWs4xnYgWxRbVlPHC9cQOcYTvM5QEbfUVKujy9kdZec71_nZWh8Zq7SppP2KB0HC9mmOt_-Oq8i3K0JKkjFk/s16000/rtp.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
12e07c5213b4a6672dccc5476c84e78c7dc2819f735f52941fc8afebcd343a63
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v437"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
1129705
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="rtp.gif"
GET
H2
200
promo.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgXFfwfq1ms-Q9qS5XSW2afQnSx-p9R84KbgEIS0dlDVsFRFWftN8SZl2J2rvdotwfvEMoDoovlsJhQA6duzBKzaKiYqvGg_zgcKGnefXMb8t7sxPcg4mWwMuaQGrEwCBQEz9GBZeVilBenjOga...
1 MB
1 MB
273ms
260ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgXFfwfq1ms-Q9qS5XSW2afQnSx-p9R84KbgEIS0dlDVsFRFWftN8SZl2J2rvdotwfvEMoDoovlsJhQA6duzBKzaKiYqvGg_zgcKGnefXMb8t7sxPcg4mWwMuaQGrEwCBQEz9GBZeVilBenjOgaXMUDuJyZshvOnrTmVh5JvJrS3uY7KP3o-4kRGZ6cJ3U/s16000/promo.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
c1a088ce29b0ff0b0156c7ddb22232029c9d12382dfb2c62b04bba67db59479e
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v437"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
1087339
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="promo.gif"
GET
H2
200
bukti.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgan1hyDd1dFZbuNNAbPJNvBSkdyx-jJmHadW1wlWvypR4e_Em1Mq-jndfld_Pzdoyg5Nw_coU6uV_GyYmCoQzNBCi9t6WnAGZNRFfFER77ILGMAoknWaUB-G7wscpVGHL9kExjh2GxwNlGCGJT...
1 MB
1 MB
330ms
317ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgan1hyDd1dFZbuNNAbPJNvBSkdyx-jJmHadW1wlWvypR4e_Em1Mq-jndfld_Pzdoyg5Nw_coU6uV_GyYmCoQzNBCi9t6WnAGZNRFfFER77ILGMAoknWaUB-G7wscpVGHL9kExjh2GxwNlGCGJT00q722xwblOlHO4YiwhFqyp8fNJ5QVpEEnW5k615UFA/s320/bukti.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
57e835e319be7437c1b26c2830fc2d401826e983c3a113f2dd1fca3fe65c6b7d
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v437"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
1180014
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="bukti.gif"
GET
H2
200
keluhan.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhxvChnmpYzmht7nKykB5ruz4PqicSJT6MqGPzPVCMKail-_JD74slebfm2LX8Pgnvn3Is5LbVfP0W2ABNh5BV8yCbpeuYOaLAwmOUv6rfV_LDq5-sjRdZCrIjM2-YmfT9dpYzmL_P5TFy5DnsZ...
1 MB
1 MB
295ms
283ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhxvChnmpYzmht7nKykB5ruz4PqicSJT6MqGPzPVCMKail-_JD74slebfm2LX8Pgnvn3Is5LbVfP0W2ABNh5BV8yCbpeuYOaLAwmOUv6rfV_LDq5-sjRdZCrIjM2-YmfT9dpYzmL_P5TFy5DnsZhAPJUwqdKMryOFFmPA3teqpbc1BfuR0izB4oGN_6LbE/s16000/keluhan.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
1a7ec5702c34c0416ff05b6186c80eda3e7752ce1fd0fa271b62839f411b868c
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v437"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
1175191
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="keluhan.gif"
GET
H2
200
2767192.png
cdn-icons-png.flaticon.com/512/2767/
15 KB
16 KB
48ms
3ms
Image
image/png
23.58.144.63
AKAMAI-ASN1 Akama...
General
Full URL
https://cdn-icons-png.flaticon.com/512/2767/2767192.png
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
23.58.144.63 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a23-58-144-63.deploy.static.akamaitechnologies.com
Software
/
Resource Hash
242b7574df69b7f8d4d0070a4b741ef1b9155ce028c505f0b97fea2de6247728

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

x-goog-metageneration
1
x-amz-meta-goog-reserved-file-mtime
1585303532
etag
"3de61968d385210a15fd87527dbaf8ef"
x-goog-stored-content-encoding
identity
x-amz-meta-x-goog-reserved-source-generation
1627233921209099
expires
Sat, 19 Jul 2025 20:33:16 GMT
x-goog-stored-content-length
15492
date
Sat, 19 Jul 2025 20:33:16 GMT
last-modified
Wed, 24 Aug 2022 13:01:29 GMT
content-type
image/png
vary
Accept-Encoding
x-default-rule
YES
cache-control
public, max-age=31536000
pragma
public
x-amz-checksum-crc32c
3BYJvQ==
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1661346089451718
content-length
15492
GET
H2
200
wk0XyUyKZL5eJW.jpg.png
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiZVX-JUoJv9sIqQNFhjWLgN28KS0LaQT7DkoSTLyPXTdzMgWM_cAN4dfsVPZllig2GpbT_PgDyoWMX85UUdCnFS0V7mIDHoWCgc6j6EFtSGghwwGnYRxhA3OABgjnlMGairJMgzrZb0xOwYS4H...
68 KB
68 KB
316ms
306ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiZVX-JUoJv9sIqQNFhjWLgN28KS0LaQT7DkoSTLyPXTdzMgWM_cAN4dfsVPZllig2GpbT_PgDyoWMX85UUdCnFS0V7mIDHoWCgc6j6EFtSGghwwGnYRxhA3OABgjnlMGairJMgzrZb0xOwYS4HtOafPqlIOo_nHfIfmqkLiLnCx9dOC_VPfUFdC2BBBNc/s1600/wk0XyUyKZL5eJW.jpg.png
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
0e084ab771422057dd4d351537103d7706acf5019b9dff17e09c870a9da6acab
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v1dc"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
69636
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="wk0XyUyKZL5eJW.jpg.png"
GET
H2
200
image_1-min.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEj7hB071KiwDIfDusXXWx-dGPK7p44euLhAOZeLUfEVKyXt4py6w5PMHRIbKXkK0CCAOBSVkzkZEqLmivzl2syt7P_sCPjFEaABK9mNCUXnuiEeebO2AINSPAgRQkWu9i1G3su4dLK4E0cSJHFQ...
44 KB
44 KB
348ms
338ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEj7hB071KiwDIfDusXXWx-dGPK7p44euLhAOZeLUfEVKyXt4py6w5PMHRIbKXkK0CCAOBSVkzkZEqLmivzl2syt7P_sCPjFEaABK9mNCUXnuiEeebO2AINSPAgRQkWu9i1G3su4dLK4E0cSJHFQdAaov0-rJcXibBIeZZMwse7d9jfYCzSFk5YanENOFmY/s1600/image_1-min.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
7e765c2504b17be43c58806872d6c4a0fc5737f6911613ec17a4945fc7aab66a
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v1e0"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
44563
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="image_1-min.jpg"
GET
H2
200
sweet%20bonan%20new.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjUFwOoajnoqGr5CKQMLXxizjDSYPN4OUkJsZHAz5A_kEu_SzkkL2_wfvOSk0MHOVAvd8alZovg2Q7trY9vIpDRQNollcI4hvUZ4GGwfFgg9wkEdiHsEeOKJPAdm2bJDqqEcvTrBqxoiamMWXjd...
35 KB
35 KB
364ms
354ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjUFwOoajnoqGr5CKQMLXxizjDSYPN4OUkJsZHAz5A_kEu_SzkkL2_wfvOSk0MHOVAvd8alZovg2Q7trY9vIpDRQNollcI4hvUZ4GGwfFgg9wkEdiHsEeOKJPAdm2bJDqqEcvTrBqxoiamMWXjd17MoHaBOqENYMSbFqp6qImD1HcakHjOOf1ZYRzF-fzQ/s1600/sweet%20bonan%20new.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
84ea548fcb5708e5d568d81bd06be83885877333c05b8d8f3378d0035f7a17e5
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v1e2"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
36051
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="sweet bonan new.jpg"
GET
H2
200
Sweet%20Bonanza%20Xmas%20New%20Logo.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjQcVFTt00oY9kLS67znZfAnU_4KdmMoUvZ3M9KYAC24VwkLoyT1FpKPx_RlOCEPIuF20zO6_Et158IEWxt_m97jBvGw5S_WwLSp34zjklUSr7uuRKp49osh2MCJb-vz4X6HpYIfsOlN1vH7V8U...
37 KB
37 KB
304ms
295ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjQcVFTt00oY9kLS67znZfAnU_4KdmMoUvZ3M9KYAC24VwkLoyT1FpKPx_RlOCEPIuF20zO6_Et158IEWxt_m97jBvGw5S_WwLSp34zjklUSr7uuRKp49osh2MCJb-vz4X6HpYIfsOlN1vH7V8UNxYaRRHoFaGyWj9p1OEpIQpWQwi084PuRZ0ybflR3qk/s1600/Sweet%20Bonanza%20Xmas%20New%20Logo.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
c0b8bb9e086cdb5d02cf833f32ac76cbd382f0bb9d0a522d704c0819c5bbbd45
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v1e4"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
37892
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="Sweet Bonanza Xmas New Logo.jpg"
GET

gatot-of-kaca.png
masuk.sgp1.cdn.digitaloceanspaces.com/images/games/
0
0


GET

pyramid-bonanza.png
masuk.sgp1.cdn.digitaloceanspaces.com/images/games/
0
0


GET
H2
200
Sugar%20Rush%20New%20Logo.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgWjD3hsUAFSgTLZjkN3PXNZ-jRmtK-nxe8KJBXJAoSGbHKAgZj50KTIzcLcofZPj307h16MXLsYm_NHQdmoI0YF0AJDsD6IjAfVzrhJ3-HXGnkHwURnVgvyuFzfR8BLPaiZOa8MdOnMc94qyck...
34 KB
34 KB
313ms
305ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgWjD3hsUAFSgTLZjkN3PXNZ-jRmtK-nxe8KJBXJAoSGbHKAgZj50KTIzcLcofZPj307h16MXLsYm_NHQdmoI0YF0AJDsD6IjAfVzrhJ3-HXGnkHwURnVgvyuFzfR8BLPaiZOa8MdOnMc94qyckhL3LWscLeVovMIqXho6WUngtza4sr9dK7reMQWpDWxg/s1600/Sugar%20Rush%20New%20Logo.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
26e1a00f0ef43c5c524e9523a26351d1f07736166d7921ec622b458a41f5b73c
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v1e6"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
34998
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="Sugar Rush New Logo.jpg"
GET
H2
200
Bonanza%20Gold%20New%20Logo.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEifjpsDOJJDQaQcw1No-qI1RrSv9xBQz8Q3bnudDkALqN_zsGJNKHhiOEE_StvVEvlET-dUKO0PsqHP9XLvlw8okt0y2GiFwAGqU16_GWrzJ3JYaDDZBYGEDbABluzafmSVvapiSquAQVeGQC6P...
32 KB
33 KB
367ms
360ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEifjpsDOJJDQaQcw1No-qI1RrSv9xBQz8Q3bnudDkALqN_zsGJNKHhiOEE_StvVEvlET-dUKO0PsqHP9XLvlw8okt0y2GiFwAGqU16_GWrzJ3JYaDDZBYGEDbABluzafmSVvapiSquAQVeGQC6PRHYlg_ynicg_ikRWqvLOdDNE-e1XTkI_sml0J2gcW7E/s1600/Bonanza%20Gold%20New%20Logo.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
b12ece59f277365ed73739c5f55c9d9ff097d137185ddeb95885249ff97c6ffa
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v1e8"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
33184
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="Bonanza Gold New Logo.jpg"
GET

aztec-gems.png
masuk.sgp1.cdn.digitaloceanspaces.com/images/games/
0
0


GET
H2
200
5%20Lions%20New%20Logo.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgCndEaqcZgberDvKVv7a_KV01mynomH7pyQwSZ_mDnJMJNqU-lPOSiVhLIODekK08i4UsOv2TQwcwm7netgbi78CtOYk6vPj7cZaa45tySnHdwHgxr3psXvmcOpBA-l8XeCuEFScxDlhjzzd1f...
54 KB
54 KB
370ms
363ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgCndEaqcZgberDvKVv7a_KV01mynomH7pyQwSZ_mDnJMJNqU-lPOSiVhLIODekK08i4UsOv2TQwcwm7netgbi78CtOYk6vPj7cZaa45tySnHdwHgxr3psXvmcOpBA-l8XeCuEFScxDlhjzzd1fXzcbulLdzM0TSDfjAtRi52o-kli1-06u9lEJAaMPWHU/s1600/5%20Lions%20New%20Logo.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
e0961859c47efed5f047049178bd6c106b198f5104dd6bdf81b301682bc98a3e
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v1ea"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
55604
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="5 Lions New Logo.jpg"
GET
H2
200
Starlight%20Chritsmas%20New%20Logo.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEg-SIsO84jegEi2jMvLtsUdF7GKGfpTnkOpr4GlR6nAHY_-_Fscvlm3a2j2Wi6B57JfqFlGR4hx1GnqhSaQOX1rpLZ1W7XUQbPVwG0u6L86d_higY5DDNQsxwnw5zrqb_Le9QCTg5eYOSyGSz5s...
39 KB
39 KB
307ms
301ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEg-SIsO84jegEi2jMvLtsUdF7GKGfpTnkOpr4GlR6nAHY_-_Fscvlm3a2j2Wi6B57JfqFlGR4hx1GnqhSaQOX1rpLZ1W7XUQbPVwG0u6L86d_higY5DDNQsxwnw5zrqb_Le9QCTg5eYOSyGSz5sfKBAUZSKD6HXzfZRdprZW_PP-ViVxRjWAbcFsh2CYKU/s1600/Starlight%20Chritsmas%20New%20Logo.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
2ba33301ad4c18efc75b8f59b9bb315ac909e06a851004460735cb6aa7213a72
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v1ec"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
39530
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="Starlight Chritsmas New Logo.jpg"
GET
H2
200
Jewel%20Rush%20New%20Logo.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjDMbC_4bPmZPmUNvvzZVND_MaA3asWbS3Cy85F53gMYIhAVHdY4MVraRJ_2OkmX7NmqitFs_TYmjcOVad0GkCKjL5az3RFXaTy_7__dU_JNj5MZf5X-zRnTvvA40SpmpKPYldU3AuhJ6BEYjwj...
33 KB
33 KB
331ms
325ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjDMbC_4bPmZPmUNvvzZVND_MaA3asWbS3Cy85F53gMYIhAVHdY4MVraRJ_2OkmX7NmqitFs_TYmjcOVad0GkCKjL5az3RFXaTy_7__dU_JNj5MZf5X-zRnTvvA40SpmpKPYldU3AuhJ6BEYjwjRUoczH0IDaQhaV3gXdSrli7qNoDAJ2Pl_TqKwgOLPCg/s1600/Jewel%20Rush%20New%20Logo.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
999ec2b7964f85511e64002f8210c9b3447307de01d212938ac0d5d8db7ef952
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v1ee"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
33358
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="Jewel Rush New Logo.jpg"
GET
H2
200
Wild%20West%20Gold%20New%20Logo.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiRQWX8Jqtcx0_-IwK_HEi-o3GuzrrrGlGS-0jz8dL2w0rk8WtsWcKiUpo6bFUROj0X1hNfOKGV7M3-GPeAjk9svY72S_dPPgQdozlkniA3RlxhrhEStWBb338WTtPspeQJ0MfGTG-fby4uk1Nw...
48 KB
49 KB
307ms
302ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiRQWX8Jqtcx0_-IwK_HEi-o3GuzrrrGlGS-0jz8dL2w0rk8WtsWcKiUpo6bFUROj0X1hNfOKGV7M3-GPeAjk9svY72S_dPPgQdozlkniA3RlxhrhEStWBb338WTtPspeQJ0MfGTG-fby4uk1NwgoG9UGY-fBByecZDgBV3IoAQ-ywip6nhXM--9JTKh90/s1600/Wild%20West%20Gold%20New%20Logo.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
45b1d3657aa9ffe34c9fc111ed09d06936e9379e5698c19d4949acf581415274
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v1f0"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
49654
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="Wild West Gold New Logo.jpg"
GET
H2
200
Wisdom%20Of%20Athena%20New%20Logo.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEj353VMlk4y0W_pYrLfmMgVORY3sZsN8ylQ_R2HG8O1nvw7HTv1MeYvm_q8n0O3k2vV01-o8mE7WczJB3w3j27V3cLJ9lxqB74ois_lKkU6ds-xWubHne6cosMmVmrQ8zICCjx8XJbumP1rp4JZ...
49 KB
49 KB
412ms
407ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEj353VMlk4y0W_pYrLfmMgVORY3sZsN8ylQ_R2HG8O1nvw7HTv1MeYvm_q8n0O3k2vV01-o8mE7WczJB3w3j27V3cLJ9lxqB74ois_lKkU6ds-xWubHne6cosMmVmrQ8zICCjx8XJbumP1rp4JZRjFTIOTO023AdqCs7FpNGG6OlPbJ7E4i2BcwVSMhUq0/s1600/Wisdom%20Of%20Athena%20New%20Logo.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
e2939ae51cd455bd9cadbd0813f183ac6ce21f453bae5903ebeb43f8e18203e8
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v1f2"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
49892
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="Wisdom Of Athena New Logo.jpg"
GET
H2
200
Santa%27s%20Great%20Gifts%20New%20Logo.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiQvWUr0AQXN-NE55Vi6O0cMgSdQ1SLojcKPj6uPDm456RseaZLyIVLHw6l77egv5h1hAg7moKxV9bnzOwS-_zp0YkS68gwKF69FCq5AohU36TFD3o0Tw9fS8Xd7ElbhDHmJDfuUxLKhw4fDD2Z...
39 KB
40 KB
314ms
309ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiQvWUr0AQXN-NE55Vi6O0cMgSdQ1SLojcKPj6uPDm456RseaZLyIVLHw6l77egv5h1hAg7moKxV9bnzOwS-_zp0YkS68gwKF69FCq5AohU36TFD3o0Tw9fS8Xd7ElbhDHmJDfuUxLKhw4fDD2Zzm0JJZdWiXqqb-33R7sMycRjp38SfzLuEqudfMuQQsw/s1600/Santa%27s%20Great%20Gifts%20New%20Logo.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
a4849987d73f343c8692c5976efb0e4f4ca25d9182ad0206c6cb2b9e7bc1539d
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v1f4"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
40437
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="Santa's Great Gifts New Logo.jpg"
GET
H2
200
Mahjong%20Ways%202%20New%20Logo.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjNng3k4aV4ZLu2-ThjcVKkYHgXhaV64MIC_NkitjzM3VMII-9hns1eahjaMtFsKDAhCmytg2eR4O7o5rvBAo5NaOdOkDdoqM96ddV8jCw-tpZh91P6g9siJLCgP_Srz2MP5Wap7fGk3B50o5lq...
43 KB
43 KB
440ms
427ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjNng3k4aV4ZLu2-ThjcVKkYHgXhaV64MIC_NkitjzM3VMII-9hns1eahjaMtFsKDAhCmytg2eR4O7o5rvBAo5NaOdOkDdoqM96ddV8jCw-tpZh91P6g9siJLCgP_Srz2MP5Wap7fGk3B50o5lqFjl2pAlPoE6QcNXDvXE9yV4ffcqtvQzjd4bcp7IYo0E/s1600/Mahjong%20Ways%202%20New%20Logo.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
5b16d38dc650b9dc34e7564e823ab67bdbc69f81d0a79e0d61c0baf788744aaa
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v1f6"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
43551
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="Mahjong Ways 2 New Logo.jpg"
GET
H2
200
Mahjong%20Ways%20New%20Logo.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiHJt8ijkeHMF9q_vBmaQwWXXCm37xvxDAzFZeyhajBjC_IeVgbkxMudnluM6XuNZwf-NH2Tml2NmTq_VAGGKvIb_MSAK6DNii0dDHkI-GJ4zisdN98P8NJhyqoXbtZ9DnWnkhrnZJZKmau0sgL...
42 KB
42 KB
350ms
338ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiHJt8ijkeHMF9q_vBmaQwWXXCm37xvxDAzFZeyhajBjC_IeVgbkxMudnluM6XuNZwf-NH2Tml2NmTq_VAGGKvIb_MSAK6DNii0dDHkI-GJ4zisdN98P8NJhyqoXbtZ9DnWnkhrnZJZKmau0sgLO6vOdrkhxzbb67sp4lonsUNbhNg8kjMA3Q--mb-kO4w/s1600/Mahjong%20Ways%20New%20Logo.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
53575d3c511655350ca6fc343a0dffa381b86cc844e5a489fc019f74ee9087c5
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v1f8"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
43379
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="Mahjong Ways New Logo.jpg"
GET
H2
200
Lucky%20Neko%20New%20Logo.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjXWxp_1_5LzK6b-jMVC7ZuU_LWPL40EKo8-ZKSZrvWK60cuijD0Xbv67wVvvmF_4Jj6yEusGYCH8HDvrXq-XjCykhkRX5RoFti3F1osWoiUaVCg263YZlAx_zo8rJ4CCGinWR-tjFv3oZFtxYs...
43 KB
43 KB
359ms
348ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjXWxp_1_5LzK6b-jMVC7ZuU_LWPL40EKo8-ZKSZrvWK60cuijD0Xbv67wVvvmF_4Jj6yEusGYCH8HDvrXq-XjCykhkRX5RoFti3F1osWoiUaVCg263YZlAx_zo8rJ4CCGinWR-tjFv3oZFtxYsFgU6ZH1_V7h7E_jRrOU-9KxdMJ5bxRcp083rNHfnd6c/s1600/Lucky%20Neko%20New%20Logo.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
42267f804c24ca4f8564f7f143a04ce6f23840ca87a89eb70df84e8aa2862e7c
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v1fa"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
43696
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="Lucky Neko New Logo.jpg"
GET
H2
200
Wild%20Bandito%20New%20Logo.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiMRKm9pwr_TE_oAlfYeL71mrj3np583skJ7z4lNoU2gaZArjqsRSiPzBSrwSCtPLinhustmURzlZNaH4RSDjIvZW-4JKNcs2xxTdSmTDtM2889k-HuP69F9vit98IF8U7zM9HrOWB7wA3ar_nz...
42 KB
43 KB
350ms
340ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiMRKm9pwr_TE_oAlfYeL71mrj3np583skJ7z4lNoU2gaZArjqsRSiPzBSrwSCtPLinhustmURzlZNaH4RSDjIvZW-4JKNcs2xxTdSmTDtM2889k-HuP69F9vit98IF8U7zM9HrOWB7wA3ar_nzs71Uv08QJmVvXABv0bfs5EasxmJt3ZWGnzMSHUyvzwo/s1600/Wild%20Bandito%20New%20Logo.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
7b1443542324668d2e448a0e87bf84adedb4cfcdcb848848a66aeb931990ba25
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v1fc"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
43413
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="Wild Bandito New Logo.jpg"
GET
H2
200
Treasure%20Of%20Aztec.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEisnoFyAXBGvb1-zTTqyuu4IUtnz8PHd9YZM5GUUBhfsVcw3YOxe-a2x1RAJRkAX1c_2IGwoXKAPMkR4LdmewUJzpNDy7P3a5kxYD-2y43P4Jio5K7iYxaS-E5uViVHCNaowtCk_f1Hqx998uMz...
42 KB
42 KB
352ms
342ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEisnoFyAXBGvb1-zTTqyuu4IUtnz8PHd9YZM5GUUBhfsVcw3YOxe-a2x1RAJRkAX1c_2IGwoXKAPMkR4LdmewUJzpNDy7P3a5kxYD-2y43P4Jio5K7iYxaS-E5uViVHCNaowtCk_f1Hqx998uMzlID_2VgT6AxAa4pvX7iAvXXbd_ftlzZXmkZpF5PAdvA/s1600/Treasure%20Of%20Aztec.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
5a7fb7e9f2768a5219181844ef6b6d35d546326f1e47af6ce2dac86634be5ea5
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v1fe"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
43279
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="Treasure Of Aztec.jpg"
GET
H2
200
Ways%20Of%20The%20Qilin%20New%20Logo.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhggmFlogTAeG6yrN4EInoKy72oVJqVvuEYJAfjKPmqKwrQVcItDxMtI6IQnUjBsh1Xkl-vR4V4bQj0gD8sU6cZfO0gfPFO1R_AHLELtSxmy2ylN6FQ1facljuGly_FYf5mjvEz4Cxes-NuvW4m...
45 KB
45 KB
355ms
346ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhggmFlogTAeG6yrN4EInoKy72oVJqVvuEYJAfjKPmqKwrQVcItDxMtI6IQnUjBsh1Xkl-vR4V4bQj0gD8sU6cZfO0gfPFO1R_AHLELtSxmy2ylN6FQ1facljuGly_FYf5mjvEz4Cxes-NuvW4mTpbiGUwKacD1qbDfVyHWtXJ9ai2dU2wX4dK1slLJuew/s1600/Ways%20Of%20The%20Qilin%20New%20Logo.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
41ccc06f3885a89caebc9f7a6b3140a24f33dbf774eeaf79ab7d74fbdec6c82c
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v200"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
45617
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="Ways Of The Qilin New Logo.jpg"
GET
H2
200
Lucky%20Clover%20Lady%20New%20Logo.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEh5qZbKDTgwya_dxX9onrwd__xLG7Njwzhtpk-UYT2-DISGeoJJZ4SztLXZE_hFNyRjTYIFWAl8_eHHwaPxvP_Bcl47PhSPpFKB6ZH4mvb1gggUdZ89U_tQEIxpt6NsGFEvHB34KBJ1dJEuPzSx...
35 KB
35 KB
403ms
395ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEh5qZbKDTgwya_dxX9onrwd__xLG7Njwzhtpk-UYT2-DISGeoJJZ4SztLXZE_hFNyRjTYIFWAl8_eHHwaPxvP_Bcl47PhSPpFKB6ZH4mvb1gggUdZ89U_tQEIxpt6NsGFEvHB34KBJ1dJEuPzSx20t4ZJ2SF6JBIaHYUOBKL35pNvvCAzVHaSJLb03wRD4/s1600/Lucky%20Clover%20Lady%20New%20Logo.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
9ed14a2ab28233a8e331466171a487ca4d5645e8a58f5a7748c3ae19dc9eff2e
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v202"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
35786
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="Lucky Clover Lady New Logo.jpg"
GET
H2
200
CaiShen%20Wins%20New%20Logo.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEh9EXfZ9ypqdFPg8uPP3K3nD6hgBIPK17pXPFPakmyd0subQjTbhJXGshL8ymUM0CWNbeXUT9eDenShjdIAGNcPKm8fkyUpD7ypmNrUPaggmnZTNTWMxqQ44Skeg2dIf1aR3qP_Ejdk-5dCbjIq...
51 KB
51 KB
373ms
365ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEh9EXfZ9ypqdFPg8uPP3K3nD6hgBIPK17pXPFPakmyd0subQjTbhJXGshL8ymUM0CWNbeXUT9eDenShjdIAGNcPKm8fkyUpD7ypmNrUPaggmnZTNTWMxqQ44Skeg2dIf1aR3qP_Ejdk-5dCbjIqYWwVffClXZzpEuOucUPXVx0rqv537YwO5sKH3VQXnig/s1600/CaiShen%20Wins%20New%20Logo.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
f83b56ef6b6b1b99aa5d9c57d51373408815b1e28a727b35a5f96de0738b9e91
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v204"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
51877
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="CaiShen Wins New Logo.jpg"
GET
H2
200
Dreams%20Of%20Macau%20New%20Logo.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhTfcSSs3kqAQ5QfGoUfRrflRg91zyjgjLA813lqFH4HgMsgjz8a_tBoF_Za-HWek0aHwq2tmBNkZTBQihPMJpySDAvt8sI37gkSga-xsB7N7_zjhNV-rqBgkXWyIx0KCmDrXLHD-3DO7bKSkmt...
38 KB
38 KB
443ms
436ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhTfcSSs3kqAQ5QfGoUfRrflRg91zyjgjLA813lqFH4HgMsgjz8a_tBoF_Za-HWek0aHwq2tmBNkZTBQihPMJpySDAvt8sI37gkSga-xsB7N7_zjhNV-rqBgkXWyIx0KCmDrXLHD-3DO7bKSkmt7vd88cV45ZG4oSr-80x2Mje7moQazrhI9g9VsyDq-rQ/s1600/Dreams%20Of%20Macau%20New%20Logo.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
03ad483edfa06ca008b7c915c2d1f9859a2a8c02ac072764e90fbf56723b2ad8
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v206"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
39061
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="Dreams Of Macau New Logo.jpg"
GET
H2
200
Super%20Golf%20Drive%20New%20Logo.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgveVnjCv0MtwSPODMX8Ao8GLhRGVNaV2eViCA3OJH_lEISm18xPspxuVBHsphN03DY_zf8WgYNsqXGM4yeNHkhPzXY0b949XAOzcjTg-iWkwgOoLlaPKN6u0oUvyUTGEYwypBkL2SCOaHpplbe...
49 KB
49 KB
419ms
412ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgveVnjCv0MtwSPODMX8Ao8GLhRGVNaV2eViCA3OJH_lEISm18xPspxuVBHsphN03DY_zf8WgYNsqXGM4yeNHkhPzXY0b949XAOzcjTg-iWkwgOoLlaPKN6u0oUvyUTGEYwypBkL2SCOaHpplbeTe4I4i1_u8zB-truiDgsjY3oIgrJcKYjZyWdaXLcBDw/s1600/Super%20Golf%20Drive%20New%20Logo.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
ed7adec770601be4ef6b7b823e4ec7f2e6005810d996960c21cca7e8af20839f
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v208"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
49986
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="Super Golf Drive New Logo.jpg"
GET
H2
200
Candy%20Bonanza%20New%20Logo.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjfB0KvKyeydd4oMV94JqC5qGVuei3iU_JZq8tDSYeXkbiO2ccXp9t_ZAq2Jl8260HAzsmQg8H7ZXromadUvhQ10v1Ayl2vfoHMa9CTbBTV72lNEMPCdcDTJaz050ToFFDuvA6O86v-_BJ78VxJ...
36 KB
36 KB
350ms
344ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjfB0KvKyeydd4oMV94JqC5qGVuei3iU_JZq8tDSYeXkbiO2ccXp9t_ZAq2Jl8260HAzsmQg8H7ZXromadUvhQ10v1Ayl2vfoHMa9CTbBTV72lNEMPCdcDTJaz050ToFFDuvA6O86v-_BJ78VxJeJ3b1492PlRrSnbEYxO08Apxld4Vct4uzsH9EmWp9zQ/s1600/Candy%20Bonanza%20New%20Logo.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
3c4de5acb67c63e93aefa4ae398c9b96b204515b0932d0be82f00edbb400b9aa
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v20a"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
36585
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="Candy Bonanza New Logo.jpg"
GET
H2
200
Cocktail%20Nights.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgqecbPZoZ1Nd0VJzv3EsY5b0L0bpsly_-GHXO3IsvFJafg5ACByZA0aVzA4mQH3vHxpgq-b8ww0KhrlIb86gxg3fyD3vrED6bLuLtb_SbQlG6DiWkJ1t6p2lY0-5zVn8OO1hG-5m367VHJuEoe...
36 KB
36 KB
356ms
350ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgqecbPZoZ1Nd0VJzv3EsY5b0L0bpsly_-GHXO3IsvFJafg5ACByZA0aVzA4mQH3vHxpgq-b8ww0KhrlIb86gxg3fyD3vrED6bLuLtb_SbQlG6DiWkJ1t6p2lY0-5zVn8OO1hG-5m367VHJuEoeoAXJbrt3o_IWYyRYqzqYlnWZHPn4fiUPuUx77nv9p8s/s1600/Cocktail%20Nights.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
72aa7aadeb336111077533c97969569bad512ab8b4af33c1c220456d3bbf9580
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v20c"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
36728
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="Cocktail Nights.jpg"
GET
H2
200
Jurassic%20Kingdom%20New%20Logo.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEggnuiwrdIwTW-6v2IUEmZWwB2RWDWTNjxG0X6H7JS_GLmOYGDJofUwr2iUqKIzoFkF71k9UoEzcKj54rfjPxi98udHJZzXNo94RNW-4zBZZao3Eb0cglc7P0aBONP1ziX3rQEfin7B_ZlDAl9Z...
54 KB
54 KB
376ms
370ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEggnuiwrdIwTW-6v2IUEmZWwB2RWDWTNjxG0X6H7JS_GLmOYGDJofUwr2iUqKIzoFkF71k9UoEzcKj54rfjPxi98udHJZzXNo94RNW-4zBZZao3Eb0cglc7P0aBONP1ziX3rQEfin7B_ZlDAl9ZrDBRuLG-uH7zC7QfywaRtxV7l6LZRf9IId5v4kEtNx4/s1600/Jurassic%20Kingdom%20New%20Logo.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
e9a92140a373ff5cc04f5e6238a71b7507480ac81df6a192636e762635f8d4d7
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v20e"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
55139
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="Jurassic Kingdom New Logo.jpg"
GET
H2
200
Supermarket%20Spree%20New%20Logo.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEju7CCYkv1kyL6etosKsvrDHzrwy-zzhqNeMBiuoj7VXnG9FGSvz0m-HVmGtQ1JY481a1Oo8DWDuJNWviLwNKgyb7TB9k6CoX3iMReR3_TxdLf5n6ECeJe0Il8G1DmB0HDDGkj9H3ya3cLDFLFn...
54 KB
54 KB
362ms
356ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEju7CCYkv1kyL6etosKsvrDHzrwy-zzhqNeMBiuoj7VXnG9FGSvz0m-HVmGtQ1JY481a1Oo8DWDuJNWviLwNKgyb7TB9k6CoX3iMReR3_TxdLf5n6ECeJe0Il8G1DmB0HDDGkj9H3ya3cLDFLFnttf6XQELgnx_lokq0lPM-bMC8FREyceGzw5xuCQzqwo/s1600/Supermarket%20Spree%20New%20Logo.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
ecaa580731d007d7caf61c28102d3bc5daaa3ff63751127cad1e3f9ac06abe0b
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v210"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
55526
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="Supermarket Spree New Logo.jpg"
GET
H2
200
Midas%20Fortune%20New%20Logo.jpg
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEj_zh1LrObfSNXvdL-F4q35-tvsfzHnJJz6kuS9pWnox4mkQQUMji1XD-5jv3R8cQm3lMJUcwY41k5nyznyG9mR-pavb50ruWO0pOnh-fc3uHXzG1jRh2WGkf70t3EjGpNTD12qO5HmGKWkVklF...
79 KB
79 KB
357ms
352ms
Image
image/jpeg
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEj_zh1LrObfSNXvdL-F4q35-tvsfzHnJJz6kuS9pWnox4mkQQUMji1XD-5jv3R8cQm3lMJUcwY41k5nyznyG9mR-pavb50ruWO0pOnh-fc3uHXzG1jRh2WGkf70t3EjGpNTD12qO5HmGKWkVklFf2YTsQa91CZT4lI34HGf4JTmRFwf02sCs_Se_t9oGSM/s1600/Midas%20Fortune%20New%20Logo.jpg
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
b725c5ba24cf4a20d1705ff7f7e75e7af666845d17c514b2041da4e4198cab77
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v212"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
80541
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/jpeg
vary
Origin
server
fife
content-disposition
inline;filename="Midas Fortune New Logo.jpg"
GET
H2
200
J0GCPtf.png
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhRHBmu_7En05hUUIaKJ1xO417KXORLt6vT-kMEW8Sz-1JeKVJdBbwyV5Ltw26Vd-gYYYortV1ry7JQWPNmPAzpMoyPXTD9aG5ZzekuB5fC3jnaBMRLkiZAGxOT8QD38_N6D9cKDt6__CM19dul...
24 KB
24 KB
373ms
368ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhRHBmu_7En05hUUIaKJ1xO417KXORLt6vT-kMEW8Sz-1JeKVJdBbwyV5Ltw26Vd-gYYYortV1ry7JQWPNmPAzpMoyPXTD9aG5ZzekuB5fC3jnaBMRLkiZAGxOT8QD38_N6D9cKDt6__CM19dulBDB4fyMLI1svNiDqN_2Qi4MpO2OvZI5bFVg4ZFaOa_k/s16000/J0GCPtf.png
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
480716d8867cf2a50d97fabcc04759e81de1259283ba3e2c4c0c1d46995dc6cd
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v448"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
24679
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="J0GCPtf.png"
GET
H2
200
J0G33YJ.png
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjGVvlX6_LlemVOWILmhIGVUPwlk5ydUO9CiROGodWiGlqZ1pKX5CjZb4-0mJI2xb9M8cRSvXLwZ_0upADJMd1LOfvR7xGcczqyeGcFCqMt_PubXLvqJFdRN3bywWGGvW0pRWOHgzeq7thGoPfu...
9 KB
9 KB
330ms
326ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjGVvlX6_LlemVOWILmhIGVUPwlk5ydUO9CiROGodWiGlqZ1pKX5CjZb4-0mJI2xb9M8cRSvXLwZ_0upADJMd1LOfvR7xGcczqyeGcFCqMt_PubXLvqJFdRN3bywWGGvW0pRWOHgzeq7thGoPfuEaYPWey-FlcH_9uDjy6ZlHYBmqQ4Dd6tUvTlOD45R08/s16000/J0G33YJ.png
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
a796080d67e5e42690ea948ab2e7d5b574f1a385e1dac5340b1d56a44f49c73c
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v448"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
9473
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="J0G33YJ.png"
GET
H2
200
J0GBJ5u.png
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgRjtbvBTRnYcnkCCDk_ZRXUQ74yKlnwUzPlcENZZtX-exiKRqrEWnwees_w1hJ0O6P1mxeeeFcBl5n7rJWa_hwMlu8P8OnWqh3sDqoHo5TSgzeHfK0keNdEHTUlbOW999HXTzhoa1uhG9bqWK4...
16 KB
17 KB
366ms
363ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgRjtbvBTRnYcnkCCDk_ZRXUQ74yKlnwUzPlcENZZtX-exiKRqrEWnwees_w1hJ0O6P1mxeeeFcBl5n7rJWa_hwMlu8P8OnWqh3sDqoHo5TSgzeHfK0keNdEHTUlbOW999HXTzhoa1uhG9bqWK4QYa862thr5jdWZfbZ6XtK0vIgTS7-J4lehE4OaOrPVQ/s16000/J0GBJ5u.png
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
1434ba0052bc740077b0f0e245abce35b1c901e9b0db19521956a70e8b3409f0
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v448"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
16855
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="J0GBJ5u.png"
GET
H2
200
J0GnXlS.png
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgRCQ925TeyVEr6S94ae5JJyzK4_rz3CMqgB5O40gSb3YqoxqEQBAOnaL-SzvJKsmfElZu6piysFngzBJUGMtzyY_l4P6tLtP8cKJIOIBrNM3l15yq1wfpOVUwSDi5TIkPcqjJFx_PtpFymtTh9...
19 KB
19 KB
339ms
335ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgRCQ925TeyVEr6S94ae5JJyzK4_rz3CMqgB5O40gSb3YqoxqEQBAOnaL-SzvJKsmfElZu6piysFngzBJUGMtzyY_l4P6tLtP8cKJIOIBrNM3l15yq1wfpOVUwSDi5TIkPcqjJFx_PtpFymtTh9_dm4SfbLg6OvPc5kwq1uk1_QEZfSn6NALzpiVOphtXE/s16000/J0GnXlS.png
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
3dc7ebef252de063ad78d19f0bf1bdbd8ebf4396c96caa919e23b9465081c70e
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v448"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
19484
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="J0GnXlS.png"
GET
H2
200
20231020-2115246.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjYI2I5klHO8ckFLV0zja5NKPQC56d-XZzlCjG943tHI8R_3c4_ZBvGV8uKoVp9vqR_k4GQ2CrSPGC2AQkD2Pe0nzFjlN6uLHcQUM4OrixjUrWFAv6bLSMmZKAnktFPDAih2oHB6PIk3jVp0g7N...
3 MB
3 MB
382ms
379ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjYI2I5klHO8ckFLV0zja5NKPQC56d-XZzlCjG943tHI8R_3c4_ZBvGV8uKoVp9vqR_k4GQ2CrSPGC2AQkD2Pe0nzFjlN6uLHcQUM4OrixjUrWFAv6bLSMmZKAnktFPDAih2oHB6PIk3jVp0g7N8FkKKdFTTGo2J5Cy5dr3IWsmYS-47oshP5QK8lb43Ac/s16000/20231020-2115246.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
23babf3b8105e414102c6bec9c2e4f6a2530d23ceae3712c305e7ee0ea6c91ad
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v44d"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
2794474
date
Sat, 19 Jul 2025 20:33:16 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="20231020-2115246.gif"
GET
H2
200
region Show response
api.livechatinc.com/global-mapper/lc_license_id/15132858/
35 B
158 B
257ms
217ms
Script
text/plain
23.32.29.106
AKAMAI-ASN1 Akama...
General
Full URL
https://api.livechatinc.com/global-mapper/lc_license_id/15132858/region?jsonp=__lc_region
Requested by
Host: cdn.livechatinc.com
URL: https://cdn.livechatinc.com/tracking.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
23.32.29.106 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a23-32-29-106.deploy.static.akamaitechnologies.com
Software
/
Resource Hash
a379b1707064386da00957301b6eb053249cfb462047d44e4fb6d52898f5b78b

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

content-length
35
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
text/plain; charset=utf-8
uber-trace-id
7030b8e4a76608a3becfef834f309ba2:76f2f1f10fa8dec8:0:1
GET
H2
200
naga-muterrrrrr-ezgif_com-gif-to-webp-converter.webp
cdn.areabermain.club/assets/cdn/az4/2024/02/12/20240212/50cc6bcd9025a0c9510bbf8fdebf62ec/
1012 KB
1014 KB
72ms
45ms
Image
image/webp
172.64.145.29
CLOUDFLARENET
General
Full URL
https://cdn.areabermain.club/assets/cdn/az4/2024/02/12/20240212/50cc6bcd9025a0c9510bbf8fdebf62ec/naga-muterrrrrr-ezgif_com-gif-to-webp-converter.webp
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.64.145.29 , Ascension Island, ASN13335 (CLOUDFLARENET, US),
Reverse DNS
Software
cloudflare /
Resource Hash
47cdc158a57807d545f39a108f30af35dfbb13d7f133abec3703f0ace15f660f
Security Headers
Name Value
Strict-Transport-Security max-age=15552000; includeSubDomains; preload

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cf-cache-status
HIT
etag
"3bac486de0225b827b87c9e6eb93725a"
age
1620
date
Sat, 19 Jul 2025 20:33:16 GMT
x-rgw-object-type
Normal
content-type
image/webp
last-modified
Wed, 02 Oct 2024 14:54:27 GMT
vary
Origin, Access-Control-Request-Headers, Access-Control-Request-Method, Accept-Encoding
x-do-cdn-uuid
0c06562b-4508-48ef-a043-0914b195365e
strict-transport-security
max-age=15552000; includeSubDomains; preload
cache-control
max-age=3600
x-amz-request-id
tx00000e6f454d74a0e4a2e-00687207c3-552f7347-sgp1b
cf-ray
961cfe2fcd27fd93-SIN
accept-ranges
bytes
content-length
1036710
server
cloudflare
GET
H2
200
_dmca_premi_badge_5.png
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEg4aiRSzvfzQ0ORBNqbZC1hzFEipo8crQGrVogkyovxMLf8jJNBKG6WpnLtRt0OnsqRB_u4f6UrW1mRRf9-bKWkI2PBvIn08WtO8LYj9SPmYq5uG15j5FR8BLXScDPPArixMllJyTPYYkRy6AX9...
6 KB
6 KB
383ms
380ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEg4aiRSzvfzQ0ORBNqbZC1hzFEipo8crQGrVogkyovxMLf8jJNBKG6WpnLtRt0OnsqRB_u4f6UrW1mRRf9-bKWkI2PBvIn08WtO8LYj9SPmYq5uG15j5FR8BLXScDPPArixMllJyTPYYkRy6AX9yrFztrzs-a_jEpvpcGuFh0S6a5jJj65AjUMJ9r-D/s135/_dmca_premi_badge_5.png
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
2a41dbcf98569ab4112d305bdaafeea3707b37c11ab842011dd86186ed1c65be
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v10e0"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
5681
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="_dmca_premi_badge_5.png"
GET
H2
200
LOGO%20END.png
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjYl9AIKmfscAMDzZO94xCIxZDgwdnQf4mUZC-TjkSyAAzn4DbneFLgyQNw-z3UYuw3KWiM7z3tIv7OuOK6dsdGjQtpgYydqh3h8WWIS_cAt_43xtWPpBcchD7rxhe1o7gWLvNuetOEslG_K4Xl...
24 KB
24 KB
382ms
381ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjYl9AIKmfscAMDzZO94xCIxZDgwdnQf4mUZC-TjkSyAAzn4DbneFLgyQNw-z3UYuw3KWiM7z3tIv7OuOK6dsdGjQtpgYydqh3h8WWIS_cAt_43xtWPpBcchD7rxhe1o7gWLvNuetOEslG_K4XlOhmQlgu5GHQIlUTTn1OxaJeYEKseqZGheTr_ap-p/w640-h36/LOGO%20END.png
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
bad488c696275e38b9e95ee1c7c8662b01705456ed3049d191fa66b0bd575cd2
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v29f"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
24900
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="LOGO END.png"
GET
H2
200
BAR%20HEADER%20QQTOTO.webp
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjLWc4gkXQkMAdzkny2qcBzm8Qv9kmetimDcNgg7wrDXrFdrTsTGy8uUhJGYPxleY4va2zOvMb2llqepXF5JGBIxQ0Uav8N6Dqon6Q46_7Iq4lGBgNuLCo5A8NC5CzyES9s2FQDgueEVFwNMZpl...
62 KB
62 KB
839ms
838ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjLWc4gkXQkMAdzkny2qcBzm8Qv9kmetimDcNgg7wrDXrFdrTsTGy8uUhJGYPxleY4va2zOvMb2llqepXF5JGBIxQ0Uav8N6Dqon6Q46_7Iq4lGBgNuLCo5A8NC5CzyES9s2FQDgueEVFwNMZplvtexSXcaj26U05szVlmxMmqUZr7-oqB7DdsaifEfNeA/s16000/BAR%20HEADER%20QQTOTO.webp
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
624bb12055fe7dc2c6bcbe9a58b27858700e0c91aac333844b96997792aeaf65
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v1c0"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
63419
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="BAR HEADER QQTOTO.png"
GET
H3
200
ALTERNATIF%20QQ.png
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgGuzpAo9OToNg7187r-WQrXGfjCIEzVnfQ8gQsCgjKWGv6usCgJxEN_Sc_ONA2uNVoJQ8N7SbbVzpUZjpx81A3ILDTFQMPHoyuNM14170VvEuf67Ht9kcnUvdhjBPJ4dTVpD1TRscJ5lEETmN3...
18 KB
18 KB
1136ms
1135ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgGuzpAo9OToNg7187r-WQrXGfjCIEzVnfQ8gQsCgjKWGv6usCgJxEN_Sc_ONA2uNVoJQ8N7SbbVzpUZjpx81A3ILDTFQMPHoyuNM14170VvEuf67Ht9kcnUvdhjBPJ4dTVpD1TRscJ5lEETmN3TLbStxI7b6eL7pgsLWfYMqsgDDrzJKrnc8V4Xa3sYcY/s16000/ALTERNATIF%20QQ.png
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
1d3aae39974bf5c4c9a42385e1ab95ea7c3c32907013dd8ebe74dbcce997377c
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v51"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
18483
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="ALTERNATIF QQ.png"
GET
H2
200
Muli.ttf
qqtotokiwi.site/assets/fonts/
48 KB
48 KB
28ms
24ms
Font
application/octet-stream
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/fonts/Muli.ttf
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
45acbaae00fb0cfa8413b582cd4c0dad9653c78a051a7215205079ccc7c7e233

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Origin
https://qqtotokiwi.site
Referer
https://qqtotokiwi.site/

Response headers

cache-control
public, max-age=14400
cf-cache-status
MISS
etag
"6466f3ae-bf70"
cf-ray
961cfe30ef313e06-SIN
expires
Sun, 20 Jul 2025 00:33:16 GMT
accept-ranges
bytes
x-cache
MISS
content-length
49008
date
Sat, 19 Jul 2025 20:33:16 GMT
content-type
application/octet-stream
last-modified
Fri, 19 May 2023 03:57:34 GMT
x-cache-hits
0
server
cloudflare
vary
Accept-Encoding
GET
H3
200
H6pKGm8W.png
imgku.io/download/
6 KB
7 KB
46ms
17ms
Image
image/png
172.67.162.223
CLOUDFLARENET
General
Full URL
https://imgku.io/download/H6pKGm8W.png
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.67.162.223 , Ascension Island, ASN13335 (CLOUDFLARENET, US),
Reverse DNS
Software
cloudflare /
Resource Hash
2cf27574ccbf4334c03240da6954708a93ff08d704c4ef850748c8c6df5936ff
Security Headers
Name Value
Strict-Transport-Security max-age=16000000; includeSubDomains; preload;
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 1; mode=block

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

ratelimit-remaining
249
cf-cache-status
HIT
etag
"1d761f8cb60e62a605f945772421cbe4"
ratelimit-reset
1
age
1979
report-to
{"endpoints":[{"url":"https:\/\/a.nel.cloudflare.com\/report\/v4?s=dCcP5PzxsqR6hFCDvFLym8jvJAUNTn074PwhMJBD%2BM%2Fk1%2Bh0hSpZOJvkxv%2BYnCe7P4rHjLdMcQUxseC5RMvyfectFUrEfqvGZiL669uyxY2REjU0%2Fg7mK2L3mw%3D%3D"}],"group":"cf-nel","max_age":604800}
x-content-type-options
nosniff
x-ratelimit-limit-second
250
x-proxy-cache
HIT
alt-svc
h3=":443"; ma=86400
server-timing
cfL4;desc="?proto=QUIC&rtt=5191&min_rtt=3627&rtt_var=2680&sent=12&recv=14&lost=0&retrans=0&sent_bytes=3709&recv_bytes=4392&delivery_rate=627586&ss_exit_cwnd=0&ss_exit_reason=0&cwnd=15457&unsent_bytes=0&cid=2a23a11e535d65f9&ts=37&inflight_dur=14&x=103"
date
Sat, 19 Jul 2025 20:33:16 GMT
x-rgw-object-type
Normal
content-type
image/png
last-modified
Wed, 06 Mar 2024 06:13:52 GMT
vary
Accept-Encoding
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=16000000; includeSubDomains; preload;
cache-control
max-age=14400
nel
{"success_fraction":0,"report_to":"cf-nel","max_age":604800}
x-ratelimit-remaining-second
249
ratelimit-limit
250
x-amz-request-id
tx000009bdbb19ff968a3a9-006865e0c1-a05b6-default
cf-ray
961cfe30bd22fd7d-SIN
accept-ranges
bytes
access-control-allow-origin
*
content-length
6022
x-xss-protection
1; mode=block
server
cloudflare
GET
H3
200
bmigDP6j.png
imgku.io/download/
4 KB
5 KB
60ms
32ms
Image
image/png
172.67.162.223
CLOUDFLARENET
General
Full URL
https://imgku.io/download/bmigDP6j.png
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.67.162.223 , Ascension Island, ASN13335 (CLOUDFLARENET, US),
Reverse DNS
Software
cloudflare /
Resource Hash
d6169df2dfb496b6e72e017e8f3c8c6e241f5db25128474e64082546e3155035
Security Headers
Name Value
Strict-Transport-Security max-age=16000000; includeSubDomains; preload;
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 1; mode=block

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

ratelimit-remaining
248
cf-cache-status
HIT
etag
"5d21a2497a856102547e2ea0782aacd7"
ratelimit-reset
1
age
855
report-to
{"endpoints":[{"url":"https:\/\/a.nel.cloudflare.com\/report\/v4?s=D6EHPoysOIboJKx%2FEG3b3lU9aTLvhpsBlglFLmvCd5w0jJ5KiVg6l%2By7zbxbeMVHas9lVGuuggsTwg0HLZGIz8tYY9hqofbX8pXJuXUQvk8vBbhsxa%2FUm1a9YA%3D%3D"}],"group":"cf-nel","max_age":604800}
x-content-type-options
nosniff
x-ratelimit-limit-second
250
x-proxy-cache
HIT
alt-svc
h3=":443"; ma=86400
server-timing
cfL4;desc="?proto=QUIC&rtt=5191&min_rtt=3627&rtt_var=2680&sent=25&recv=14&lost=0&retrans=0&sent_bytes=19136&recv_bytes=4392&delivery_rate=627586&ss_exit_cwnd=0&ss_exit_reason=0&cwnd=15457&unsent_bytes=0&cid=2a23a11e535d65f9&ts=41&inflight_dur=19&x=103"
date
Sat, 19 Jul 2025 20:33:16 GMT
x-rgw-object-type
Normal
content-type
image/png
last-modified
Wed, 06 Mar 2024 06:13:28 GMT
vary
Accept-Encoding
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=16000000; includeSubDomains; preload;
cache-control
max-age=14400
nel
{"success_fraction":0,"report_to":"cf-nel","max_age":604800}
x-ratelimit-remaining-second
248
ratelimit-limit
250
x-amz-request-id
tx000005c358e720f6129c7-00682e87d8-a7921-default
cf-ray
961cfe30bd24fd7d-SIN
accept-ranges
bytes
access-control-allow-origin
*
content-length
4542
x-xss-protection
1; mode=block
server
cloudflare
GET
H3
200
VB208XyC.png
imgku.io/download/
8 KB
9 KB
47ms
19ms
Image
image/png
172.67.162.223
CLOUDFLARENET
General
Full URL
https://imgku.io/download/VB208XyC.png
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.67.162.223 , Ascension Island, ASN13335 (CLOUDFLARENET, US),
Reverse DNS
Software
cloudflare /
Resource Hash
373c4996ffff18406b9e4ee2ea524168ea17965804e7500925f975b4c21f1de4
Security Headers
Name Value
Strict-Transport-Security max-age=16000000; includeSubDomains; preload;
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 1; mode=block

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

ratelimit-remaining
249
cf-cache-status
HIT
etag
"3e35d0568f0f022c10241d3527adf2cc"
ratelimit-reset
1
age
2414
report-to
{"endpoints":[{"url":"https:\/\/a.nel.cloudflare.com\/report\/v4?s=V7dO5iKeSqsegQsCiJtKUlurvoOMFjG6ZRQ3W1SdS3RoJjLU2%2B7MH%2BfSD6vT%2BjVTidQn0i%2FSOcTBsrxtTW%2FilcjWHx0iTdEh%2FrLuqQ2J5JQfhL%2BZ9gexuCyHlg%3D%3D"}],"group":"cf-nel","max_age":604800}
x-content-type-options
nosniff
x-ratelimit-limit-second
250
x-proxy-cache
HIT
alt-svc
h3=":443"; ma=86400
server-timing
cfL4;desc="?proto=QUIC&rtt=5191&min_rtt=3627&rtt_var=2680&sent=18&recv=14&lost=0&retrans=0&sent_bytes=10807&recv_bytes=4392&delivery_rate=627586&ss_exit_cwnd=0&ss_exit_reason=0&cwnd=15457&unsent_bytes=0&cid=2a23a11e535d65f9&ts=39&inflight_dur=16&x=103"
date
Sat, 19 Jul 2025 20:33:16 GMT
x-rgw-object-type
Normal
content-type
image/png
last-modified
Wed, 06 Mar 2024 06:12:58 GMT
vary
Accept-Encoding
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=16000000; includeSubDomains; preload;
cache-control
max-age=14400
nel
{"success_fraction":0,"report_to":"cf-nel","max_age":604800}
x-ratelimit-remaining-second
249
ratelimit-limit
250
x-amz-request-id
tx000000408d4502f3294e9-00686f1f48-a2c45-default
cf-ray
961cfe30bd23fd7d-SIN
accept-ranges
bytes
access-control-allow-origin
*
content-length
8622
x-xss-protection
1; mode=block
server
cloudflare
GET
H3
200
CXYtrpdy.png
imgku.io/download/
6 KB
7 KB
54ms
26ms
Image
image/png
172.67.162.223
CLOUDFLARENET
General
Full URL
https://imgku.io/download/CXYtrpdy.png
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.67.162.223 , Ascension Island, ASN13335 (CLOUDFLARENET, US),
Reverse DNS
Software
cloudflare /
Resource Hash
be2842f543dc56cb96df830123192738fd492fe990fd69dbec12270fabc5bbfe
Security Headers
Name Value
Strict-Transport-Security max-age=16000000; includeSubDomains; preload;
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 1; mode=block

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

ratelimit-remaining
249
cf-cache-status
HIT
etag
"f296e761b7f0e082fef0e49ef767fafe"
ratelimit-reset
1
age
3390
report-to
{"endpoints":[{"url":"https:\/\/a.nel.cloudflare.com\/report\/v4?s=C8e4ztHb3%2F67DDQ4qyPAWDmp%2Fw1FNrBmSYE5EzKJ5%2BJ730ClCd4uPhVXNTssjTkITQ%2BqEtBmojWGrbtn6JV3QfIi%2BeDgoCFWfhRJ9tdw3smT%2FKu1faFYZyCE3g%3D%3D"}],"group":"cf-nel","max_age":604800}
x-content-type-options
nosniff
x-ratelimit-limit-second
250
x-proxy-cache
HIT
alt-svc
h3=":443"; ma=86400
server-timing
cfL4;desc="?proto=QUIC&rtt=5191&min_rtt=3627&rtt_var=2680&sent=18&recv=14&lost=0&retrans=0&sent_bytes=10807&recv_bytes=4392&delivery_rate=627586&ss_exit_cwnd=0&ss_exit_reason=0&cwnd=15457&unsent_bytes=0&cid=2a23a11e535d65f9&ts=39&inflight_dur=16&x=103"
date
Sat, 19 Jul 2025 20:33:16 GMT
x-rgw-object-type
Normal
content-type
image/png
last-modified
Wed, 06 Mar 2024 06:10:59 GMT
vary
Accept-Encoding
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=16000000; includeSubDomains; preload;
cache-control
max-age=14400
nel
{"success_fraction":0,"report_to":"cf-nel","max_age":604800}
x-ratelimit-remaining-second
249
ratelimit-limit
250
x-amz-request-id
tx00000444f6c9063845e49-00686f1a3f-a058e-default
cf-ray
961cfe30bd25fd7d-SIN
accept-ranges
bytes
access-control-allow-origin
*
content-length
5952
x-xss-protection
1; mode=block
server
cloudflare
GET
H3
200
PAV.png
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiznkRokzoRft-LcptB-StdjBO00bJUaeP_C9AgVTdrEckwcXgUiOoL_EpwFqmtg-8718z5WhGk4xPE8Rex5NqL5zX3KfQGzYUJya-bVVCvcoz6RS-_JgqNnangRwa8p84xWHFaqbBr5ZgE1Ebi...
14 KB
14 KB
546ms
545ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiznkRokzoRft-LcptB-StdjBO00bJUaeP_C9AgVTdrEckwcXgUiOoL_EpwFqmtg-8718z5WhGk4xPE8Rex5NqL5zX3KfQGzYUJya-bVVCvcoz6RS-_JgqNnangRwa8p84xWHFaqbBr5ZgE1EbiHPttBhLUTww2LEoJNULBIEMm4sHbUTzNyBkufxm_XlQ/s16000/PAV.png
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
b5ad811f2f5be0756f9ca9df4bc094c4734131774801af0c0e00322bbef218b6
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v26"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
13974
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="PAV.png"
POST
H2
204
collect
www.google-analytics.com/g/
0
0
35ms
12ms
Fetch
text/plain
142.251.10.113
GOOGLE
General
Full URL
https://www.google-analytics.com/g/collect?v=2&tid=G-SSN8YGQCHV&gtm=45je57g1v9172514708za200&_p=1752957196505&gcd=13l3l3l3l1l1&npa=0&dma=0&tag_exp=101509157~103116026~103200004~103233427~104684208~104684211~104952206~104952208&cid=374633845.1752957197&ul=en-sg&sr=1600x1200&uaa=&uab=&uafvl=&uamb=0&uam=&uap=&uapv=&uaw=0&are=1&frm=0&pscdl=noapi&_s=1&sid=1752957197&sct=1&seg=0&dl=https%3A%2F%2Fqqtotokiwi.site%2F&dt=QQTOTO%20%3A%20the%20best%20place%20to%20play%20online%20slot%20and%20casino%20games%20in%20Indonesia%202025&en=page_view&_fv=1&_nsi=1&_ss=1&_ee=1&tfd=947
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtag/js?id=G-SSN8YGQCHV
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.10.113 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
sd-in-f113.1e100.net
Software
Golfe2 /
Resource Hash

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cache-control
no-cache, no-store, must-revalidate
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
content-security-policy-report-only
script-src 'none'; form-action 'none'; frame-src 'none'; report-uri https://csp.withgoogle.com/csp/scaffolding/ascnsrsggc:102:0
report-to
{"group":"ascnsrsggc:102:0","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/scaffolding/ascnsrsggc:102:0"}],}
expires
Fri, 01 Jan 1990 00:00:00 GMT
access-control-allow-origin
https://qqtotokiwi.site
cross-origin-opener-policy-report-only
same-origin; report-to=ascnsrsggc:102:0
content-length
0
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sat, 19 Jul 2025 20:33:17 GMT
content-type
text/plain
server
Golfe2
GET
H2
200
get_dynamic_configuration Show response
api.livechatinc.com/v3.6/customer/action/
385 B
601 B
260ms
257ms
Script
application/javascript
23.32.29.106
AKAMAI-ASN1 Akama...
General
Full URL
https://api.livechatinc.com/v3.6/customer/action/get_dynamic_configuration?x-region=us-south1&license_id=15132858&client_id=c5e4f61e1a6c3b1521b541bc5c5a2ac5&url=https%3A%2F%2Fqqtotokiwi.site%2F&channel_type=code&jsonp=__gsou7vqqkwb
Requested by
Host: cdn.livechatinc.com
URL: https://cdn.livechatinc.com/tracking.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
23.32.29.106 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a23-32-29-106.deploy.static.akamaitechnologies.com
Software
/
Resource Hash
06a8853c839d6f33460be962c875acda97272820a211581017d806981b3d343e
Security Headers
Name Value
Content-Security-Policy frame-ancestors https://qqtotokiwi.site/;
X-Frame-Options allow-from https://qqtotokiwi.site/

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

content-security-policy
frame-ancestors https://qqtotokiwi.site/;
content-length
385
date
Sat, 19 Jul 2025 20:33:17 GMT
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
cross-origin-resource-policy
cross-origin
x-frame-options
allow-from https://qqtotokiwi.site/
GET
H2
200
loader.css
qqtotokiwi.site/css/components/
3 KB
1 KB
18ms
16ms
Stylesheet
text/css
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/css/components/loader.css
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/js/auth/login.js?v=c3syfye1yivoif3u4mel
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
2f75efe3c598d795e95fade1746451bb15e1e950724f34155195d4d6e93180ae

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

server
cloudflare
cache-control
public, max-age=2592000
content-encoding
gzip
cf-cache-status
MISS
etag
W/"6466f3b1-b86"
cf-ray
961cfe33789f3e06-SIN
expires
Mon, 18 Aug 2025 20:33:17 GMT
accept-ranges
bytes
x-cache
MISS
content-length
1028
date
Sat, 19 Jul 2025 20:33:17 GMT
content-type
text/css
last-modified
Fri, 19 May 2023 03:57:37 GMT
vary
Accept-Encoding
x-cache-hits
0
GET
H2
200
search-icon-png-0.png
www.freeiconspng.com/uploads/
17 KB
17 KB
739ms
352ms
Image
image/png
78.46.22.9
HETZNER-AS Hetzne...
General
Full URL
https://www.freeiconspng.com/uploads/search-icon-png-0.png
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
78.46.22.9 Falkenstein, Germany, ASN24940 (HETZNER-AS Hetzner Online GmbH, DE),
Reverse DNS
static.9.22.46.78.clients.your-server.de
Software
nginx/1.18.0 (Ubuntu) /
Resource Hash
7ea9463fbd40b0522d7f911faba3d5d87ad8de6c4d75e08cfbf907c6e098c27b

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cache-control
no-cache, must-revalidate
etag
"58c879c4-4437"
accept-ranges
bytes
content-length
17463
date
Sat, 19 Jul 2025 20:33:18 GMT
content-type
image/png
last-modified
Tue, 14 Mar 2017 23:16:20 GMT
server
nginx/1.18.0 (Ubuntu)
GET
H3
200
hfB1x4vQ.json Show response
imgku.io/download/
7 KB
2 KB
860ms
852ms
XHR
application/json
172.67.162.223
CLOUDFLARENET
General
Full URL
https://imgku.io/download/hfB1x4vQ.json
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/assets/js/jquery-2.2.4.min.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.67.162.223 , Ascension Island, ASN13335 (CLOUDFLARENET, US),
Reverse DNS
Software
cloudflare /
Resource Hash
01ec6b9344c49b01b68053ba12874ee4440b31e569a8838ee5eb702846ab1986
Security Headers
Name Value
Strict-Transport-Security max-age=16000000; includeSubDomains; preload;
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 1; mode=block

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Accept
application/json, text/javascript, */*; q=0.01
Referer
https://qqtotokiwi.site/

Response headers

ratelimit-remaining
249
content-encoding
zstd
cf-cache-status
DYNAMIC
etag
W/"9529a5c19ef34bf7ad66422e53b5701a"
ratelimit-reset
1
report-to
{"endpoints":[{"url":"https:\/\/a.nel.cloudflare.com\/report\/v4?s=KgEiOWcq2Dro2VKkoq8KugYjESpQDTos%2BFrB%2Fcy%2BIWij%2BwWhQgMaKd13Yeosdcy2N8%2B7Dqiaw7W%2F5tQsJpXlpu%2BkNJ%2F%2FqcuS5R98RyQJabp%2B7goWHlV7688o%2Bg%3D%3D"}],"group":"cf-nel","max_age":604800}
x-content-type-options
nosniff
x-ratelimit-limit-second
250
x-proxy-cache
HIT
alt-svc
h3=":443"; ma=86400
server-timing
cfL4;desc="?proto=QUIC&rtt=3509&min_rtt=2879&rtt_var=1323&sent=10&recv=10&lost=0&retrans=0&sent_bytes=3630&recv_bytes=3252&delivery_rate=3007623&ss_exit_cwnd=0&ss_exit_reason=0&cwnd=15456&unsent_bytes=0&cid=3d4ea0415e0ccd84&ts=852&inflight_dur=39&x=103"
date
Sat, 19 Jul 2025 20:33:18 GMT
x-rgw-object-type
Normal
content-type
application/json
last-modified
Fri, 07 Mar 2025 04:43:18 GMT
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=16000000; includeSubDomains; preload;
nel
{"success_fraction":0,"report_to":"cf-nel","max_age":604800}
x-ratelimit-remaining-second
249
ratelimit-limit
250
x-amz-request-id
tx0000091bc85c798f62332-0067caa6f5-a50e7-default
cf-ray
961cfe33ea325fdb-SIN
access-control-allow-origin
*
x-xss-protection
1; mode=block
server
cloudflare
GET
H3
200
hfB1x4vQ.json Show response
imgku.io/download/
7 KB
0
858ms
858ms
XHR
application/json
172.67.162.223
CLOUDFLARENET
General
Full URL
https://imgku.io/download/hfB1x4vQ.json
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/assets/js/jquery-2.2.4.min.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.67.162.223 , Ascension Island, ASN13335 (CLOUDFLARENET, US),
Reverse DNS
Software
cloudflare /
Resource Hash
01ec6b9344c49b01b68053ba12874ee4440b31e569a8838ee5eb702846ab1986
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 1; mode=block

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Accept
application/json, text/javascript, */*; q=0.01
Referer
https://qqtotokiwi.site/

Response headers

ratelimit-remaining
249
content-encoding
zstd
cf-cache-status
DYNAMIC
etag
W/"9529a5c19ef34bf7ad66422e53b5701a"
ratelimit-reset
1
report-to
{"endpoints":[{"url":"https:\/\/a.nel.cloudflare.com\/report\/v4?s=KgEiOWcq2Dro2VKkoq8KugYjESpQDTos%2BFrB%2Fcy%2BIWij%2BwWhQgMaKd13Yeosdcy2N8%2B7Dqiaw7W%2F5tQsJpXlpu%2BkNJ%2F%2FqcuS5R98RyQJabp%2B7goWHlV7688o%2Bg%3D%3D"}],"group":"cf-nel","max_age":604800}
x-content-type-options
nosniff
x-ratelimit-limit-second
250
x-proxy-cache
HIT
alt-svc
h3=":443"; ma=86400
server-timing
cfL4;desc="?proto=QUIC&rtt=3509&min_rtt=2879&rtt_var=1323&sent=10&recv=10&lost=0&retrans=0&sent_bytes=3630&recv_bytes=3252&delivery_rate=3007623&ss_exit_cwnd=0&ss_exit_reason=0&cwnd=15456&unsent_bytes=0&cid=3d4ea0415e0ccd84&ts=852&inflight_dur=39&x=103"
date
Sat, 19 Jul 2025 20:33:18 GMT
x-rgw-object-type
Normal
content-type
application/json
last-modified
Fri, 07 Mar 2025 04:43:18 GMT
x-frame-options
SAMEORIGIN
nel
{"success_fraction":0,"report_to":"cf-nel","max_age":604800}
x-ratelimit-remaining-second
249
ratelimit-limit
250
x-amz-request-id
tx0000091bc85c798f62332-0067caa6f5-a50e7-default
cf-ray
961cfe33ea325fdb-SIN
access-control-allow-origin
*
x-xss-protection
1; mode=block
server
cloudflare
GET
H3
200
sasasa.png
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhVVp_8UGaNffPc3w6dl84mEfeRHMesnW3_wERq2g60OkN_S2p3qCHmHG3ZLMPXmBXoHp19WSkjA7x_KsPlMICR29G51xQPR998I4grraikBi3a4dm9dRZ3h9DSIuhnW_GKW8maC6kFDA_odIso...
43 KB
43 KB
1063ms
1059ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhVVp_8UGaNffPc3w6dl84mEfeRHMesnW3_wERq2g60OkN_S2p3qCHmHG3ZLMPXmBXoHp19WSkjA7x_KsPlMICR29G51xQPR998I4grraikBi3a4dm9dRZ3h9DSIuhnW_GKW8maC6kFDA_odIsoyCjekWhG2PE0OXKUeChPEHo_C9cwfaXRK7PceC26OaI/s16000/sasasa.png
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
8bbe4c8b419311ed94a24330552c10ed14983465b5c82613ab5d2d74fcca4e9a
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v490"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
44511
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="sasasa.png"
GET
H3
200
bca%20on.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgm47uGgIeBRSfVBL2MFx-orosMAQ53-EcJWZn0U5PVyLZXz-oZ90DsCRaVGe-Zq_blvFusGIZHBndKwymqUxI66rBttqqcgDP5yHvpnqu3weUj2suzFQMmpjKXy6CGJfHNOHBIyM9u_rZPaf1n...
227 KB
227 KB
1105ms
1100ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgm47uGgIeBRSfVBL2MFx-orosMAQ53-EcJWZn0U5PVyLZXz-oZ90DsCRaVGe-Zq_blvFusGIZHBndKwymqUxI66rBttqqcgDP5yHvpnqu3weUj2suzFQMmpjKXy6CGJfHNOHBIyM9u_rZPaf1nq_1J-YxQ9GR8jHyoLdWq9SRz_8uHkdbves56Q8sxs8g/s16000/bca%20on.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
c0ace412ca1cc23ec09d653937cdcd8672bda7aefdeddc330262b3c7bb833f22
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v1ae"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
232628
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="bca on.gif"
GET
H3
200
mandiri%20on.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhnMqVmxZZJ92RHPNMlSKec9upOZg8XLo5gm6eIetqXoepVqn-QQAFPXpn5WVw_ekJSeGYKCkM7TKPWb9db0UYP6ywk0U9vZYhiXBZfWb6sozrYHpf06AY_MOk6b9szucj1xQxYOrxYIVCl-X1i...
286 KB
286 KB
865ms
857ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhnMqVmxZZJ92RHPNMlSKec9upOZg8XLo5gm6eIetqXoepVqn-QQAFPXpn5WVw_ekJSeGYKCkM7TKPWb9db0UYP6ywk0U9vZYhiXBZfWb6sozrYHpf06AY_MOk6b9szucj1xQxYOrxYIVCl-X1i4FITTzDZc__tewC4kBQ6shiHYxBsSANqsDLH-GDjeoE/s16000/mandiri%20on.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
39fc7afde669d336af3d05eb3f9d58c42deef014e7f1a62e2d231b2b06ab88bc
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v1ae"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
292486
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="mandiri on.gif"
GET
H3
200
bri%20on.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEi2rW_GkhoTH2GWAE3-zZwg9Qr19F2Zsia6l5LaPhOmVAixayro9XML0XwpRVPbbIIzSztN3fHZCa6g4JaomFc0ZMMLrHuwvXuB0yFiZGd4rM1hNX-9gKXbOJg6EMd6-vxGVcFnfcSNiU_Ta0dk...
265 KB
265 KB
1080ms
1074ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEi2rW_GkhoTH2GWAE3-zZwg9Qr19F2Zsia6l5LaPhOmVAixayro9XML0XwpRVPbbIIzSztN3fHZCa6g4JaomFc0ZMMLrHuwvXuB0yFiZGd4rM1hNX-9gKXbOJg6EMd6-vxGVcFnfcSNiU_Ta0dkQhSddh1i6WzbJTlzHu-rqFXFTVy-1XzUEfWhKtT4_64/s16000/bri%20on.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
925c5f504b1c681a841eef511ec610622626d728a8c5ac51dbe79d9251de1c88
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v1ad"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
271194
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="bri on.gif"
GET
H3
200
bni%20on.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjE4fLWcz-4SImEdiyWrnwOoHaTGJ6831BAaG2YLQ1Y2FKjqMsxy7CeLEYeT9ywG7aBdxZaOtO0CPjxf_P-LqQE25HuXKfupLfO6duAMPyFSlt8cKs-jmIvRl6zwEQ-rNfETVMvqkvcQhYZs2f8...
284 KB
284 KB
1050ms
1044ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjE4fLWcz-4SImEdiyWrnwOoHaTGJ6831BAaG2YLQ1Y2FKjqMsxy7CeLEYeT9ywG7aBdxZaOtO0CPjxf_P-LqQE25HuXKfupLfO6duAMPyFSlt8cKs-jmIvRl6zwEQ-rNfETVMvqkvcQhYZs2f86vU0rHT60VcP6FK-gjhGbvIwbE6Sf-Hs4ynCYgdrGAE/s16000/bni%20on.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
6ab9b998562575fb94fd0ca515cc9e41510748c81bd9817ec256d92198370919
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v1ad"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
291198
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="bni on.gif"
GET
H3
200
ovo%20on.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhJFb9musphbaR94Nq1ABOC5IamJgleZur47PPb2OkHL97FXsHksyzV1ZdkvBIirM5rRROxd8WqxYZntv0lliL0gMXPfWh7sO8N3XhUj7EBU1ddWUPy3oZV0Tm6x4uOEk0fmXxZimyvZDBgRhM7...
211 KB
211 KB
858ms
853ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhJFb9musphbaR94Nq1ABOC5IamJgleZur47PPb2OkHL97FXsHksyzV1ZdkvBIirM5rRROxd8WqxYZntv0lliL0gMXPfWh7sO8N3XhUj7EBU1ddWUPy3oZV0Tm6x4uOEk0fmXxZimyvZDBgRhM7D4P6EjwNGTzeSwVmL69uHph9ifp1xt8y_BJvTTkkLxE/s16000/ovo%20on.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
9fd10c2231584196fe8da4c4246b0c00296a137cc2f472fb247eb5c0044aa444
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v1ae"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
216194
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="ovo on.gif"
GET
H3
200
gopay%20on.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjV6-BkkUvU_Nky8VpmAuJehfpmmQahO1XP5j2BgB11fPZwoPwEhfH7-RlYYCptQzeTV3a36ZASoP8nru9TG5S3r4xvEn8fKroV_i6fJtRQzPdRYr_QInKVNHnAkUHTFD-ARAbexQht5loXEEKg...
224 KB
224 KB
1143ms
1140ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjV6-BkkUvU_Nky8VpmAuJehfpmmQahO1XP5j2BgB11fPZwoPwEhfH7-RlYYCptQzeTV3a36ZASoP8nru9TG5S3r4xvEn8fKroV_i6fJtRQzPdRYr_QInKVNHnAkUHTFD-ARAbexQht5loXEEKgDdy1cKPj3vFII2iWJFRxJ4875fhS9XjEAN2hCDYhr5w/s16000/gopay%20on.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
05293928ea5187dc9cb2b18f7e32ebb6bf4450888aa413b98551217108c0ea61
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v1ae"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
228872
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="gopay on.gif"
GET
H3
200
dana%20on.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjIs9y_8IylAnMcx2N2LKcx2POg0y_RmOdNNKkYbTuT4JfJP7WYFkDY5amcs8tJaNiVEJoCniZJPElCDnuHjCBCadGqTuVNBKn95_h2iNnWgQScgBkHCYKGK_Fb8dWc5lwmC1r8Gp579PkEHUGb...
273 KB
273 KB
845ms
841ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjIs9y_8IylAnMcx2N2LKcx2POg0y_RmOdNNKkYbTuT4JfJP7WYFkDY5amcs8tJaNiVEJoCniZJPElCDnuHjCBCadGqTuVNBKn95_h2iNnWgQScgBkHCYKGK_Fb8dWc5lwmC1r8Gp579PkEHUGbFSpquJ33XV0E3UrIAQrXiZM5dPZjuufMmibxNl6elJg/s16000/dana%20on.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
53198ad95b9eb6ef70ec8f46c1da1ef3d17e7c22557c8fbecbf0aeb6090c80c8
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v1ae"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
279423
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="dana on.gif"
GET
H3
200
sgp.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEj2NSoJ0vtkhMzitX27mdFSF_tV9WRerEQ3pE37eqsABkCA_uqvvuTgsQcIYCjadUGPtUlp2V9SCRKf3F-ZZQcniwCt3JjwnZIQbo96daosNE1Z83DxPcHvkaf7wYt8bpZFgG_LgemyJfCjd4X8...
81 KB
81 KB
893ms
868ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEj2NSoJ0vtkhMzitX27mdFSF_tV9WRerEQ3pE37eqsABkCA_uqvvuTgsQcIYCjadUGPtUlp2V9SCRKf3F-ZZQcniwCt3JjwnZIQbo96daosNE1Z83DxPcHvkaf7wYt8bpZFgG_LgemyJfCjd4X8GSfKDQQsm-2SFgtjX58_7I0FMVVQT-JMgyx9yVVerEo/s1600/sgp.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
9b9a493c7bd4e52c7d5980ea409e80f34d8d57b1cd999e67cad4d1650dc8275a
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v163"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
82445
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="sgp.gif"
GET
H3
200
hongkong.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhwuP0fAShqHsmGsTezDu6uWMY-J57G5NR03DsuJKDp1QixZYvF1PMMB1RGDkFr3LQzgXExuZYBtpAnYJjOZIgqUwTmDz4JoU4bMb3W5_ui4VZc_vvSaKZ892aTzlz0lJtpsEL1xfq6xgnBivc6...
79 KB
79 KB
893ms
867ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhwuP0fAShqHsmGsTezDu6uWMY-J57G5NR03DsuJKDp1QixZYvF1PMMB1RGDkFr3LQzgXExuZYBtpAnYJjOZIgqUwTmDz4JoU4bMb3W5_ui4VZc_vvSaKZ892aTzlz0lJtpsEL1xfq6xgnBivc6_4uerGcN809_S0NzgGG-wYee_dxzBww2rOYSadoJe7I/s1600/hongkong.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
f5350b0f80f32d5b89efdaf67ca24d790a9960dd1e8bd371f97fb84d3be7d9b0
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v166"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
80393
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="hongkong.gif"
GET
H3
200
china.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjk50dccjUWPExryildpc75IdLNQTvBcnq0cqPff0ASVxEt13XkNagajOywGg258SWCk-YK4aLIvoJnz-QnLbPT3vlLd8wJtruZXBMh5mhUtbK6T50zz92fxMrao9zPvnjc791AefLzK5Ufruzb...
61 KB
61 KB
1063ms
1039ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjk50dccjUWPExryildpc75IdLNQTvBcnq0cqPff0ASVxEt13XkNagajOywGg258SWCk-YK4aLIvoJnz-QnLbPT3vlLd8wJtruZXBMh5mhUtbK6T50zz92fxMrao9zPvnjc791AefLzK5Ufruzb8ud0v9fE-2yyuqjzdj5nQmLpX0yYOX_6VNlvs1f1Y9g/s1600/china.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
efdc406eb4651d150e5b3729c3abd97da3f35c8370f78e45f5c6adef8a93f4be
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v165"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
62243
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="china.gif"
GET
H3
200
bullseye.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjRQjxf_-FmBE02e-awYNPq-RvRP-0kT0DVfa75f6cFVUT0tuId_TJTFdPiJBOHaxX1QnMHy1OuirVzWoI1lR8JSJqQ69r78CZo68ggdE7aPX7RaAdRJ-M6X8nneZ3J1hXnw1-yOut4bfn3WbwR...
78 KB
78 KB
1144ms
1122ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjRQjxf_-FmBE02e-awYNPq-RvRP-0kT0DVfa75f6cFVUT0tuId_TJTFdPiJBOHaxX1QnMHy1OuirVzWoI1lR8JSJqQ69r78CZo68ggdE7aPX7RaAdRJ-M6X8nneZ3J1hXnw1-yOut4bfn3WbwR5TI_zShBoZjDkmqLtYNzAzUbd-fSl71QCIPCMgXVOfU/s1600/bullseye.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
49a26f1b764c3e81b6b831b1fdb642868e6afbdfe79341fd29ee3b08347847a0
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v166"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
79429
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="bullseye.gif"
GET
H3
200
cambodia.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjwNvQ7n8Z76RqSEYmf_xyEgQR-BLUBhxBV0E-Mp5-7X2aSBlv6t2hfzJIJ34JB7Xh4XrBrC3yRPdy6UWKuUQ9y6NgUppViMoeCKHidUwtkWc2PiBHJKlk-GXvLn242-a1ZUlMV8u6FHTV4eOmU...
70 KB
70 KB
1223ms
1199ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjwNvQ7n8Z76RqSEYmf_xyEgQR-BLUBhxBV0E-Mp5-7X2aSBlv6t2hfzJIJ34JB7Xh4XrBrC3yRPdy6UWKuUQ9y6NgUppViMoeCKHidUwtkWc2PiBHJKlk-GXvLn242-a1ZUlMV8u6FHTV4eOmUpoDK9Nt0BW0EV2OL9e1GH82LiH2Aw0tbH0ArCnwnU7Y/s1600/cambodia.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
d598c8d0887f398f5e3464aa37a2bd77cdff2f9d0d846b2d91a86fe85610cf8b
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v166"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
71828
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="cambodia.gif"
GET
H3
200
callifornia.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgu4PkFvQwdDMEJnvuIyEo4CMT36GMxiujkyN9hoK2Pz8WwdTiyUr6RRtx7ZeENoDnmKzto9X4bJ_RioYd00k-SiweQvXZNc6TFx9Dvq5P5ATUN9p3kjhGS2RDvC761LMKfI1K34MX0gwMrTxLf...
77 KB
77 KB
877ms
854ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgu4PkFvQwdDMEJnvuIyEo4CMT36GMxiujkyN9hoK2Pz8WwdTiyUr6RRtx7ZeENoDnmKzto9X4bJ_RioYd00k-SiweQvXZNc6TFx9Dvq5P5ATUN9p3kjhGS2RDvC761LMKfI1K34MX0gwMrTxLf9Kq490C0bpqIb-xjQWpNkOVLp6KoyGUNnZvBBhBbcXg/s1600/callifornia.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
45cc85f50998d7695e5f219ba3348a7ef4ba407bcb36bbd7fd8191acf9ade8a7
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v164"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
79205
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="callifornia.gif"
GET
H3
200
carolina.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgRhMTKlboVviUuSIdrUL25ndtdViGntxN2TFr_VQnZwAYZhCov29WdtdtVUnqvmVgqhg0E5QWo70xx4bUbIpnK5yxeodST_WSZW8HeZjLB4lim5tbZlDzqTNBufJc9xO_xcsMQahx4-Ecr8mzt...
73 KB
74 KB
989ms
966ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgRhMTKlboVviUuSIdrUL25ndtdViGntxN2TFr_VQnZwAYZhCov29WdtdtVUnqvmVgqhg0E5QWo70xx4bUbIpnK5yxeodST_WSZW8HeZjLB4lim5tbZlDzqTNBufJc9xO_xcsMQahx4-Ecr8mztHnwskdc-RJXvm4j2Nr3h4Wq5MYv73Efod2zIToQIppk/s1600/carolina.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
cdb2cf36dee34d0495c09e2601bcd528ba63e01da77c3fa4adef8ae34944cd70
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v165"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
75257
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="carolina.gif"
GET
H3
200
florida.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiW2ZiMqZAooIldA_JiEIpQMDFCpo7eHiOt0lmciuuKGJiIMAljpXsZXLpmfVFMT1E7gzGzruFrDFvIYVpz8J7B3UOm9lHpJqtv2BIuHGZZNfg0DNCi-fRBYE8YErB33gPuieeSD8i3_Jdajhj0...
70 KB
70 KB
924ms
902ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiW2ZiMqZAooIldA_JiEIpQMDFCpo7eHiOt0lmciuuKGJiIMAljpXsZXLpmfVFMT1E7gzGzruFrDFvIYVpz8J7B3UOm9lHpJqtv2BIuHGZZNfg0DNCi-fRBYE8YErB33gPuieeSD8i3_Jdajhj0MdskXLRvEg_rn6qNt4cykkYiZqYFc0Bx7nPhOZqx-2k/s1600/florida.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
ddd7216743eaedad035bc59bb6f92a22b5758e370f5ad7417bf55df663a20803
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v164"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
71808
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="florida.gif"
GET
H3
200
illionis.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgs3Creqs-pExJN_dZQVr3nK2d6ntqiJXxDtJhq1ZohkcSD2nBkdQTKdkuH_2rII5OqamRzfeju7FqciDLeqW7DhyphenhyphenH4LfAdcneT_gitUBY3NEnimBuUd5AzjqZk2RgtmOcY7Ttyru...
68 KB
68 KB
945ms
923ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgs3Creqs-pExJN_dZQVr3nK2d6ntqiJXxDtJhq1ZohkcSD2nBkdQTKdkuH_2rII5OqamRzfeju7FqciDLeqW7DhyphenhyphenH4LfAdcneT_gitUBY3NEnimBuUd5AzjqZk2RgtmOcY7TtyruPh2ysqSzIfQ62aVlAMQdnPro45sscDwlQh3xq7E5cTo7WpHiJoBIY/s1600/illionis.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
1cb5bcfaff8d285c2f72b11cd0565f3aac6859db3faee815dc2c37cbc06146c9
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v165"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
69669
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="illionis.gif"
GET
H3
200
jakarta.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEj09d7vl5Z2TeYAuuFjrQz8Cdx2fgWhLXRoQsdHiPfqy-wCgXaF5bHBWN-n2hbpmdwtNQRcQFBpqOzMOLex1RgHgP3uTT_Os85mch4N2gJsCcU85fw-m00T3dwC4s70crk7rZFeWaFgo5BYGfLN...
61 KB
61 KB
943ms
922ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEj09d7vl5Z2TeYAuuFjrQz8Cdx2fgWhLXRoQsdHiPfqy-wCgXaF5bHBWN-n2hbpmdwtNQRcQFBpqOzMOLex1RgHgP3uTT_Os85mch4N2gJsCcU85fw-m00T3dwC4s70crk7rZFeWaFgo5BYGfLNB8LgGI5G1nNrWzG0bv__nKhnQmZ_lgiXLNfkcZcVjx8/s1600/jakarta.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
f4f4ef3240cbb7a3ff76c04a500ec97afda047be3de676cf4640400bac651773
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v165"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
62697
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="jakarta.gif"
GET
H3
200
jepang.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhaHilvOv0WYFxm5q9zdMWdQKK_R8NUlw2KpaqF1KognIbpNyQHviNngVdi0fyuKaVhbhfKPDn0SDT_fJWI2Yx08QhfD0BcvGX_jSlyK-R9DD3Apq6yv4_ceOxl2kEpzdI2n1JaOQdnWvHm9eO3...
59 KB
59 KB
1189ms
1167ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhaHilvOv0WYFxm5q9zdMWdQKK_R8NUlw2KpaqF1KognIbpNyQHviNngVdi0fyuKaVhbhfKPDn0SDT_fJWI2Yx08QhfD0BcvGX_jSlyK-R9DD3Apq6yv4_ceOxl2kEpzdI2n1JaOQdnWvHm9eO3ekhDkfdU8sUw0cweau17ctMQb7jsg_6tZbL7teKwU_Q/s1600/jepang.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
ab0a5172b61d1425fe64a91df72ae29f2baf35a7b5b678dfb994781b715309a7
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v167"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
60366
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="jepang.gif"
GET
H3
200
japan%20pools.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhtp0UAVaVitq2_nPOTutsymOG7bvHN01gStm_utwKph2q9JP3hYqrt6gIIV9lNqXW8UciDEpFYNrilLzt4kVnWHG5hJddkQk9EJENFvtYr92sJVrIR3PrmVkcR5QPFrERXiuHAgdwWOr7wIXhi...
97 KB
97 KB
858ms
837ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhtp0UAVaVitq2_nPOTutsymOG7bvHN01gStm_utwKph2q9JP3hYqrt6gIIV9lNqXW8UciDEpFYNrilLzt4kVnWHG5hJddkQk9EJENFvtYr92sJVrIR3PrmVkcR5QPFrERXiuHAgdwWOr7wIXhibdiR5h7W3kGQ_PxqK7qcoMHl8IrZC0B9m5ij8A61re8/s1600/japan%20pools.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
85513a5018b7431d4bc6e4743004682883c61c18fef2f889b332b61fd6f4ff8e
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v163"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
99519
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="japan pools.gif"
GET
H3
200
kentucky.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgSkbDb0kiiJ3DaJccs8WeHGGGCVYGtVrokyUSRBsLKolv9jzoOujhufNjpaTfYPPAKrzgtjht0B1LV_OX9JmYKOB9XMgq34MnU7ATijF5oIUmS6ryMSpmDd0Qor92g9cAfF6ruLqh4dKk_Zh8v...
74 KB
74 KB
954ms
933ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgSkbDb0kiiJ3DaJccs8WeHGGGCVYGtVrokyUSRBsLKolv9jzoOujhufNjpaTfYPPAKrzgtjht0B1LV_OX9JmYKOB9XMgq34MnU7ATijF5oIUmS6ryMSpmDd0Qor92g9cAfF6ruLqh4dKk_Zh8vKrI6Y_btbrxkJpiD7cXvdfQ6TejPSbMVuxShGKa7pbs/s1600/kentucky.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
3b7aab0ffdf2bff2d0eb0c6441b5c59a4a125a999c08471517e23ca9a05fcb24
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v166"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
75940
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="kentucky.gif"
GET
H3
200
korea.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEigsfWCGo30mLewR5Lx6zrK3ILgNO3XFdsq3TYojY5iiPoJKqiPyDCrQNthD6WxAV_FKpLlGbpBQY0tQiY2fofV0BRqchKUpBdLqguDvUVgvIKWW12ROKB0NizsmxtvMryfkGMsMA_MBlSChUYI...
65 KB
65 KB
894ms
873ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEigsfWCGo30mLewR5Lx6zrK3ILgNO3XFdsq3TYojY5iiPoJKqiPyDCrQNthD6WxAV_FKpLlGbpBQY0tQiY2fofV0BRqchKUpBdLqguDvUVgvIKWW12ROKB0NizsmxtvMryfkGMsMA_MBlSChUYICBEpFgmVU079Hh5dap2S939PoeXjXee7m7SQi-iT26w/s1600/korea.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
8471a9d93167c8749a7d3592aa1d3603d4398a519712e176918004b21783f888
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v165"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
66731
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="korea.gif"
GET
H3
200
KINGKONG.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhzt_HvR5eW8P5V7r0smA8cMBX96AVlhEhFxBKkZqAbBq5T2VsGgpP9Q427rzBrfVQoObDeMTe1fmOIforGRJwzgOJKwH2uMas-PlrZ_Rnp899vD4dTHp3cIMytI0cMT_BUFkCOFlQyDrSNoVOz...
80 KB
80 KB
1143ms
1123ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhzt_HvR5eW8P5V7r0smA8cMBX96AVlhEhFxBKkZqAbBq5T2VsGgpP9Q427rzBrfVQoObDeMTe1fmOIforGRJwzgOJKwH2uMas-PlrZ_Rnp899vD4dTHp3cIMytI0cMT_BUFkCOFlQyDrSNoVOz4JUwCN13pCflkqQ3JtHqsDtjO4RmKyURkp1fwlb-SMM/s1600/KINGKONG.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
7b709c330e9b8e972a00555a1e6f03c77ebbbfd167312c36efe22b208b047d90
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v163"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
82251
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="KINGKONG.gif"
GET
H3
200
kupang.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgZee7Bndseu1PQmFseH8RGK2myK9PTSMC9gTB1BWy13TMS8Aps6Pyg8u8hHliGO5gfvvN11xBbiSQkYlZFsb2wHNQUYKpKgwImO0cx_zwiiBpNPpQaBDLlXtAppFuSI_3ETlowVQEkJQoj4es_...
62 KB
62 KB
916ms
896ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgZee7Bndseu1PQmFseH8RGK2myK9PTSMC9gTB1BWy13TMS8Aps6Pyg8u8hHliGO5gfvvN11xBbiSQkYlZFsb2wHNQUYKpKgwImO0cx_zwiiBpNPpQaBDLlXtAppFuSI_3ETlowVQEkJQoj4es_NRFKIlfRlLzjxsSEri-WJ7o6fRClWWxXwoNGx5c_c48/s1600/kupang.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
7dce1c4a3bf340cc03d5e65996820a2c972c7dba7975b3084a71a25ff144046a
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v166"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
63408
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="kupang.gif"
GET
H3
200
missouri.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhLML-dcW-Mgy6L8nIpqlGPUquPqrIrcsIDjoyVMknVHA_xmeb6CrAGLwuvic1WyolqHErvEZ7pcNuppqd5csaQGQRVb84q1i_6ZzQQBKMbHfKVmImglbMBcRS8sBma8s5kRNR-Q5fosodCDekB...
74 KB
74 KB
894ms
874ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhLML-dcW-Mgy6L8nIpqlGPUquPqrIrcsIDjoyVMknVHA_xmeb6CrAGLwuvic1WyolqHErvEZ7pcNuppqd5csaQGQRVb84q1i_6ZzQQBKMbHfKVmImglbMBcRS8sBma8s5kRNR-Q5fosodCDekBPpZdvDXEAK0Pa71i0JO_A9GhpZFm0vNt8V5h97JHnWk/s1600/missouri.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
f280c2fc7c6f0c3cdb80160a91bebbdd3fed81bf46a55f5e1689dacffcf3b8e6
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v163"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
75635
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="missouri.gif"
GET
H3
200
new%20jersey.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgX7zIgNp_oVb9c2J-kPbgNjRJ-XhpHeirsGZM3b8q-tEk6w9O08IOERYon0YpNUvmmFHsmIOHFEBDSXicsa36J0EUu4FU13CUrrji1yWG0wwmsM0px_prhm_uquR7j6TX-251P23hMFG0I-ARK...
74 KB
74 KB
969ms
948ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgX7zIgNp_oVb9c2J-kPbgNjRJ-XhpHeirsGZM3b8q-tEk6w9O08IOERYon0YpNUvmmFHsmIOHFEBDSXicsa36J0EUu4FU13CUrrji1yWG0wwmsM0px_prhm_uquR7j6TX-251P23hMFG0I-ARKogiwgI3oSerh7_Fvd3pnOQqcGP4drBWE5gzzDYy1sm4/s1600/new%20jersey.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
3af52c81706f514c13476a4bbe38e792d3dada08fd7ab0acb946277c175f959f
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v163"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
76131
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="new jersey.gif"
GET
H3
200
new%20york.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhfG0FZK9INBwVZifr0mN_XogI6XgFGt8AsO5RmBQ3l6UxW4nrKjLEBn5HbPY0KLStSYvOcHW3dlbx3wVftd2icVeqClgUUNw5aczNTmwiCLRrgKpXL3_sk2sxPKeqNsTVQaDnz7x6gvmGxtOnx...
75 KB
76 KB
907ms
886ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhfG0FZK9INBwVZifr0mN_XogI6XgFGt8AsO5RmBQ3l6UxW4nrKjLEBn5HbPY0KLStSYvOcHW3dlbx3wVftd2icVeqClgUUNw5aczNTmwiCLRrgKpXL3_sk2sxPKeqNsTVQaDnz7x6gvmGxtOnx_OUCKaQsAtIEKiOheZIBW_1fWV2r2PF6XggpE1NEA2I/s1600/new%20york.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
230d2621d167db30fd785686ab9cfc012bbcffd63a6c46a35a56d6ecbd21c330
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v166"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
77291
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="new york.gif"
GET
H3
200
nusa%20pools.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiG0atu2V52zgvwGK2AeML_7TDuqrPqvUkxAxWGUXajYP_7HS-HpDcQAEBLOMqYcxYHj0AifDnZ-yboHwj5C5epEgORADK9IOB4nC3Z5WWOt_K3K87Pwzd5h-A4wzQWGV7usxePHuBnkAkrF2Eh...
73 KB
73 KB
980ms
959ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiG0atu2V52zgvwGK2AeML_7TDuqrPqvUkxAxWGUXajYP_7HS-HpDcQAEBLOMqYcxYHj0AifDnZ-yboHwj5C5epEgORADK9IOB4nC3Z5WWOt_K3K87Pwzd5h-A4wzQWGV7usxePHuBnkAkrF2EhNINdLGvxU4trgTLS1Wb0Tx2pGO0CMxe4PXI7TVfHzt0/s1600/nusa%20pools.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
d794236461f2a50e252c3a5ab3230fc1fa42d7b5bc4084077931e7d4a03067b6
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v164"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
74358
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="nusa pools.gif"
GET
H3
200
nusa%20toto.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjTK_Q68qP-sWUiFLVNWRVlENBJCTtsGReMN0FLlPSudVzRsoNR9j5lRTT8bgVU4-5DpJmstX5lP1U4XH2k6dO1Bc0HAPikLPn5Wg-ddpvoKtmZYxnekDaB_Q2SUsuPklz8pbBZditSf7f-NLA6...
70 KB
70 KB
1041ms
1020ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjTK_Q68qP-sWUiFLVNWRVlENBJCTtsGReMN0FLlPSudVzRsoNR9j5lRTT8bgVU4-5DpJmstX5lP1U4XH2k6dO1Bc0HAPikLPn5Wg-ddpvoKtmZYxnekDaB_Q2SUsuPklz8pbBZditSf7f-NLA6v0T8JwSf1fT9KSjPcPP-FVLqtg0OeNMdv38bhrDEBQY/s1600/nusa%20toto.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
3fc91417ca2b2f55d5f1947f8eea9d27398e9f0d1b13f078a5d16a8a2d9368f1
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v165"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
71992
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="nusa toto.gif"
GET
H3
200
oregon.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhF5bTDaczjUgAolEzLVezXhwWc2Nwc5v0peCM9DpNJw-qqBruj6bKZIgV5NW8WQkwNNrCsyb19McIFse3xk64Slc4Uaepz2heuQxld-oivTtqkvHudTJHIHWHKNn3l_R0VYi0vLk7f-mLXx_2y...
73 KB
73 KB
1032ms
1010ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhF5bTDaczjUgAolEzLVezXhwWc2Nwc5v0peCM9DpNJw-qqBruj6bKZIgV5NW8WQkwNNrCsyb19McIFse3xk64Slc4Uaepz2heuQxld-oivTtqkvHudTJHIHWHKNn3l_R0VYi0vLk7f-mLXx_2yjtSqba2-_pWczdaICTKzEITnm2e4tZPglikS3_QEPqk/s1600/oregon.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
bbf01f68b51763c5e87b9dd472a6e585a32aceb4c51a034d7e8353d6b32d4f38
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v163"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
75004
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="oregon.gif"
GET
H3
200
pcso.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiMdq29HcUpyVWWrEErp_7Lq0YzRKyl44XT8UI3vK7ZdEh6LdhJNowfMZv-D5m6LX9YcuaS-XGKlCuOHsbyG4_eX42oGhRmhmwvBbbGYLfOHQMgMOaCaDAxIKleJNlMRQ85oA3e4DsVnRraUQYS...
62 KB
62 KB
910ms
889ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiMdq29HcUpyVWWrEErp_7Lq0YzRKyl44XT8UI3vK7ZdEh6LdhJNowfMZv-D5m6LX9YcuaS-XGKlCuOHsbyG4_eX42oGhRmhmwvBbbGYLfOHQMgMOaCaDAxIKleJNlMRQ85oA3e4DsVnRraUQYS4dYzHg0NQ6_m-Q7oJpVLZEcLv437_Bw79aBNgbw7Ed4/s1600/pcso.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
c2384f36a74df3707f44499728e72a777bd3fd2b430caf7d4b0701e711d0b8f2
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v164"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
63153
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="pcso.gif"
GET
H3
200
rhode%20island%20mid.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEh39zLtDZuqnH9vw5mQ7vB3KqNtCl7_jhld5-U01k6G4XKHLsL0NC6hDlO7KyJHTHL19jQokqU8VSoKsnUJYzlV8ZFBZonlNA-pYc5KmjP9HMnWw96gwNIINQpH54WWuVNOYJr6oOD0Cg6x3tpi...
88 KB
88 KB
978ms
957ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEh39zLtDZuqnH9vw5mQ7vB3KqNtCl7_jhld5-U01k6G4XKHLsL0NC6hDlO7KyJHTHL19jQokqU8VSoKsnUJYzlV8ZFBZonlNA-pYc5KmjP9HMnWw96gwNIINQpH54WWuVNOYJr6oOD0Cg6x3tpidqJ_TnnQhITrKvfedRFyuFeg02jRxby-6ruQ0ZkLRIA/s1600/rhode%20island%20mid.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
3a64937a464b2179a78e9d35bb372d2394293a9bd32f398f4e655ddfcd70a53b
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v164"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
89832
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="rhode island mid.gif"
GET
H3
200
sydney.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEg_V0m29Ijb3RYKo3aPCGIr0OInCapRRdH-h3PfEZ4ZjIRoMgDUr8K9WnDgRaXk3G9XehmHqR25jBoltSehUJvDbNHWikRLFTe_a8AIkGt-67wsOjO-628oHAnkNMXMUxfCWg9D7GWdDbU28maN...
65 KB
65 KB
920ms
900ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEg_V0m29Ijb3RYKo3aPCGIr0OInCapRRdH-h3PfEZ4ZjIRoMgDUr8K9WnDgRaXk3G9XehmHqR25jBoltSehUJvDbNHWikRLFTe_a8AIkGt-67wsOjO-628oHAnkNMXMUxfCWg9D7GWdDbU28maNwm966_JPIdSzsde5wTebzVm2_96UaLh11I8dWQh-SQA/s1600/sydney.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
03faeb81ae851f321e7b231c7cdf0d5974508e0f3678736e8d896399df9de811
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v164"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
66520
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="sydney.gif"
GET
H3
200
taiwan.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiJKPDFbXa4fdeZ6pUIJjrgvSDQSxhxFwPjYQdre_YVdPKPhyphenhyphenJW_O3hczqHsCYcOadNmY5DQFn0hIXpoPs1k07mdro-svxNz37IIJ3iP4A8XnEoRqpUM-hq_BAHHsyKieyEzlJ5uT...
64 KB
64 KB
969ms
949ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiJKPDFbXa4fdeZ6pUIJjrgvSDQSxhxFwPjYQdre_YVdPKPhyphenhyphenJW_O3hczqHsCYcOadNmY5DQFn0hIXpoPs1k07mdro-svxNz37IIJ3iP4A8XnEoRqpUM-hq_BAHHsyKieyEzlJ5uTnSdK96zYrf4lgXxxhiOiVHNoWnllKcUgr5S-hA2Nj3C82dtFkVyv8/s1600/taiwan.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
34a8ce7851064d39b82eb6b4a3ae4ae9c868ffec2c5b013fce13db1236bc22a0
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v166"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
65864
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="taiwan.gif"
GET
H3
200
tennessee.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhB2T659xHxVr8ycK3j2Hg45bcODoObTWcyC1bAWCJv0lf3jdEEBhVtakrJ3oaDpWTo0_tfu_2EyTtdliy8_y4ztGj5bO4edxAsfyVgv6e0HAiB0rafW72k3XqSZqQWaW06nU3O3z6joCnLDRav...
71 KB
71 KB
830ms
810ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhB2T659xHxVr8ycK3j2Hg45bcODoObTWcyC1bAWCJv0lf3jdEEBhVtakrJ3oaDpWTo0_tfu_2EyTtdliy8_y4ztGj5bO4edxAsfyVgv6e0HAiB0rafW72k3XqSZqQWaW06nU3O3z6joCnLDRav8pGQaYPFjP_KEHWUz87xxOKbj1nh1AMwbQZIcnEfWr0/s1600/tennessee.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
90b8ed7f6774107032908ca66b18cd62374f85d4c0b607bbabc8e2bc00464483
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v164"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
72624
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="tennessee.gif"
GET
H3
200
texas.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhH8RyMwf2z8dYo9fp3hMgMO7xjrsswUF1FZKD2Emp7xGUCvroKcNl8bJWJ5eP57BPRG-QFxHR16iS3iO0c49ALeMHTcqm2IyPzyybY_q6ua3FAV2_QpS3cB08l6BpfbhuMPXw6sWkLC04DETLH...
65 KB
65 KB
1076ms
1057ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhH8RyMwf2z8dYo9fp3hMgMO7xjrsswUF1FZKD2Emp7xGUCvroKcNl8bJWJ5eP57BPRG-QFxHR16iS3iO0c49ALeMHTcqm2IyPzyybY_q6ua3FAV2_QpS3cB08l6BpfbhuMPXw6sWkLC04DETLHhBwBqlwDMUCeiOQ5AnVw8AhJfHemT5pDC5oUTxcPefU/s1600/texas.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
3be5d62f547bb6c65785303b2fb1bdf8dd1d0fdb6f25d10213fcff54bcd7a357
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v166"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
66583
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="texas.gif"
GET
H3
200
totomacau.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgfN0mRvd7KoiiNNTyyzOMue9g1qXCdpxcje-49598ifNl62zarWSCkqwZl67dnreSeHjwGVq_YyIT7xn-ttlBxjnQzKMZvcXB18Fwxv9tj1IuQEfXwoXS8OvPBve7Dl_lZHb83ayoXVklnwQsS...
75 KB
75 KB
1126ms
1107ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgfN0mRvd7KoiiNNTyyzOMue9g1qXCdpxcje-49598ifNl62zarWSCkqwZl67dnreSeHjwGVq_YyIT7xn-ttlBxjnQzKMZvcXB18Fwxv9tj1IuQEfXwoXS8OvPBve7Dl_lZHb83ayoXVklnwQsSDU1Ok7dAjzJ6v0VbRIAoHuwrZ5Tw6qX8IW1Jy4WK8L4/s1600/totomacau.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
c3bd5f5a73de3e19fbfdd13cca576b1d17b6d84e3a9a7cece9efd4726899f1f1
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v166"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
76824
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="totomacau.gif"
GET
H3
200
virginia.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEi0EOEF4F-74QwW0VB8WWjWXY660iaax2xTg5db9VQKBNjI5gMwIbcL1Lv6CdWM3Lfdlz_6XvFxhc08Xl3R6ofOTRPei99QhfvDBZFi_INg_W4ycUkk0xrCE7OK09_NgtC_dPHmWf2G0YrQDBG7...
72 KB
72 KB
1090ms
1072ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEi0EOEF4F-74QwW0VB8WWjWXY660iaax2xTg5db9VQKBNjI5gMwIbcL1Lv6CdWM3Lfdlz_6XvFxhc08Xl3R6ofOTRPei99QhfvDBZFi_INg_W4ycUkk0xrCE7OK09_NgtC_dPHmWf2G0YrQDBG7ZnZMHjypfb-Z4s54M-_u2FZvmltftnmNCz85cYGLKuY/s1600/virginia.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
8d1d81653665b6167ced0670807c2fce6370e8aa0d48767f6a68f6cf1148d8b7
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v165"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
73471
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="virginia.gif"
GET
H3
200
Top%20trend.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhLko0qyFCv7bxHhaURTd8ue6gf-InQgQWKJYFRn-Jw0HWrFPJDPBrlVmKST5PxHdszfVNxf4O0Hvzz7laJAhJ7Ol58GNg-Nj0vOcC8XYGRGhzw8UYQeUUjINgG9Wfqs1FmSi9Wbp9akbwGpEcE...
89 KB
89 KB
1084ms
1066ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhLko0qyFCv7bxHhaURTd8ue6gf-InQgQWKJYFRn-Jw0HWrFPJDPBrlVmKST5PxHdszfVNxf4O0Hvzz7laJAhJ7Ol58GNg-Nj0vOcC8XYGRGhzw8UYQeUUjINgG9Wfqs1FmSi9Wbp9akbwGpEcECKpeyO8Y1uJmqRpaR-Ru4-0PiRHNt_Ffbe3eKcvk_VE/s1600/Top%20trend.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
18fecb314e57ea301647fb7dc124e46ce11e8bda6a9cf73d4f368a6ce8d9d746
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v163"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
91231
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="Top trend.gif"
GET
H3
200
sicbo%20ball.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEg-7Z1_whbpSbRsFeqt0iiB_R7cXErgTBinH6X8vCLc1cq0X0sTjzWY0n_QldNAXMpL3I8eKNJz2tLa1qESVWo3UPys8sponhyxdNu4hA1b6NbpjPr1rTdhRvI6pJ5EgP5f4SF9CKJpBxPyASeB...
85 KB
85 KB
925ms
907ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEg-7Z1_whbpSbRsFeqt0iiB_R7cXErgTBinH6X8vCLc1cq0X0sTjzWY0n_QldNAXMpL3I8eKNJz2tLa1qESVWo3UPys8sponhyxdNu4hA1b6NbpjPr1rTdhRvI6pJ5EgP5f4SF9CKJpBxPyASeBsa_uLtXiTbOFVCT3JbPgp1WXroKNEC3L38juTDXaFu4/s1600/sicbo%20ball.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
9cfc116f10c364fbd87b3f19a857da113ede59aedf1de28af2b87ec6902e6c17
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v163"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
87419
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="sicbo ball.gif"
GET
H3
200
suwit.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgfA0gwC6JOB3ORANubgkFuxYbeqYeT7P6icAeWEks_qCot1ThXJPvv0bjSx-y5eJUZeP1xfSFBpKGWTj42H2Gp135J4s9Y_IkELL_ZkwEyr036U2c_reMiJBHZietUt98ssGfCowmSu7KH-SJQ...
60 KB
60 KB
1140ms
1122ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgfA0gwC6JOB3ORANubgkFuxYbeqYeT7P6icAeWEks_qCot1ThXJPvv0bjSx-y5eJUZeP1xfSFBpKGWTj42H2Gp135J4s9Y_IkELL_ZkwEyr036U2c_reMiJBHZietUt98ssGfCowmSu7KH-SJQDTGTwhWXqlScqBnasslbU3dO6mqHIsU1rsc5sKf1uvA/s1600/suwit.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
3959c050f2dc63d06764e3394c3190068e60e6c168ebe9a532e6d61c9dfe0530
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v164"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
61565
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="suwit.gif"
GET
H3
200
red%20white.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiNiyOjeQPwqYMdKR8RFgutkIjzqtCOTwxaSrVrKWC54wtpnhp2Ny0OlgCXkGrnfj91izS1HurCX3OoepeRvUP8aqOsSYninEVukAY686JHo_m8817OQDSc5GrEAqe1je2B2IRQrdTDhRoDcp9K...
71 KB
71 KB
1004ms
979ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiNiyOjeQPwqYMdKR8RFgutkIjzqtCOTwxaSrVrKWC54wtpnhp2Ny0OlgCXkGrnfj91izS1HurCX3OoepeRvUP8aqOsSYninEVukAY686JHo_m8817OQDSc5GrEAqe1je2B2IRQrdTDhRoDcp9KtzEjiTNvnWXkPJuW91krBYDnu7CT7j9PqM6rtdpSkDA/s1600/red%20white.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
d23aab8e833179400063e1973b4ed9d50cb39ba302bb99ebb1c1779a1e2c1715
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v164"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
72747
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="red white.gif"
GET
H3
200
roulette%20(2).gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhA1VWbvbdFzNKxGB-DdC9tBe8IDvZx6WbrRQRrs4Cdc0yTYdhZSPKEA4Sm084oqtjxlu2a_JYM5etyvKBtQRjo8ChmCnEhSkFCtvkmFV-Dx9QnUKY9FrT2__CzpvoAW_5p2j6T9xDaVxGnGtNc...
84 KB
84 KB
1159ms
1126ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhA1VWbvbdFzNKxGB-DdC9tBe8IDvZx6WbrRQRrs4Cdc0yTYdhZSPKEA4Sm084oqtjxlu2a_JYM5etyvKBtQRjo8ChmCnEhSkFCtvkmFV-Dx9QnUKY9FrT2__CzpvoAW_5p2j6T9xDaVxGnGtNcBpqtbCrvNhntrTVjrINNn619B2Wiyv41OU9a85g4YiQ/s1600/roulette%20(2).gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
5b3ae7f7234863a0775b214bdeaa9f44aa4a3e06163e03486f45ab8067e90b0f
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v165"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
85886
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="roulette (2).gif"
GET
H3
200
race%20ball.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgE2TA9jSOOLGVzCy8hdyOSsVx8lTIuDQeZjTwlirstePu7SA1xuuoS9oWyc-SLDstJZnjxwasNgaeIzEhVUgOtJzimlLaryonQH-OhRw-qttw9o1hyphenhyphenJDYPsglTykplp6gijSE13I...
73 KB
73 KB
926ms
892ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgE2TA9jSOOLGVzCy8hdyOSsVx8lTIuDQeZjTwlirstePu7SA1xuuoS9oWyc-SLDstJZnjxwasNgaeIzEhVUgOtJzimlLaryonQH-OhRw-qttw9o1hyphenhyphenJDYPsglTykplp6gijSE13I6s0QwOaqVxObLupwpU-x80p8kl6YB31nDTXemjSAjkuXzMvdGcDys/s1600/race%20ball.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
66c48e4e8b96b3ff0550da8ffa663d51b52337dfc7df544544499f769cef5dcf
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v166"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
74850
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="race ball.gif"
GET
H3
200
pragmatic.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgKNyUfEVdXnr_VDdBDjxO9kxQMCVCqt1QbH1BfJKfjCXzLvcvlYrDzjFWKL0Rz68DwCS5l3-rznRY4o4xLujbMTwTXmpLmKkrTEzJXytiDRwGyuWxzPFA43Go9h3Af-z3mXuN4nmdER7r2Kn8h...
98 KB
98 KB
962ms
930ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgKNyUfEVdXnr_VDdBDjxO9kxQMCVCqt1QbH1BfJKfjCXzLvcvlYrDzjFWKL0Rz68DwCS5l3-rznRY4o4xLujbMTwTXmpLmKkrTEzJXytiDRwGyuWxzPFA43Go9h3Af-z3mXuN4nmdER7r2Kn8h2r-wzL1VZReKU7UcLv6-dx9y4QbGDhCWMc8bYgkltrM/s1600/pragmatic.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
2317595b2f5391bfa05f57b2557c1d361131dc6392f1957f396b99b4865731da
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v163"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
100131
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="pragmatic.gif"
GET
H3
200
pg%20soft.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiyIbjvq-c6_1LllaP-44jyWFzqezPvG451CRkF0QJ4NgdjFfa996liyjjRZJ_fpIPCe1snFQ5INtp0TXCTlVhOw2Ye4DX6EC5vWqw9fBBxWLOuJtfjNv6JqfQMvHbhFH2szdCDDthwiCL374dL...
107 KB
107 KB
980ms
948ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiyIbjvq-c6_1LllaP-44jyWFzqezPvG451CRkF0QJ4NgdjFfa996liyjjRZJ_fpIPCe1snFQ5INtp0TXCTlVhOw2Ye4DX6EC5vWqw9fBBxWLOuJtfjNv6JqfQMvHbhFH2szdCDDthwiCL374dLmNHNHLVcIqCScE0CdBVp0qSsZB3_DPNmPvoVCXYiY3I/s1600/pg%20soft.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
08a9718be96d0c889d30ba490bd7c570a61d0fc90ebd170a42c9d856d2f29ac1
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v163"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
109736
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="pg soft.gif"
GET
H3
200
oglok.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEivtA16uDRWAWNNnSt8X5NwAJ7VaHmSKda6HSYtd0K0WuhWvcvtg9id4dS_qxIktjQzvgdmLs5eGFipwODYCDYWXAhAAAQ2JkH81H-qNxPI2k4IHZNGKPu9-9CftPL0a-2aFlZAPH00yECKYig_...
69 KB
69 KB
1092ms
1060ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEivtA16uDRWAWNNnSt8X5NwAJ7VaHmSKda6HSYtd0K0WuhWvcvtg9id4dS_qxIktjQzvgdmLs5eGFipwODYCDYWXAhAAAQ2JkH81H-qNxPI2k4IHZNGKPu9-9CftPL0a-2aFlZAPH00yECKYig_HNFtCzLAgaxp-7syHgo2o4qKybRliu9iSmY_eqpilyk/s1600/oglok.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
b47d1aa45797ad3e5d33d3ad0dbc0485308e8e4fd034794288d77f64d1050a04
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v166"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
70347
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="oglok.gif"
GET
H3
200
nolimit%20city.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiWhlJtKuqut1nJiSXcf5w9K1G5T6zfLNTs9CJkOPVNVlpd-9xb1oLSXHu5WlzvBlBkV7TYLdeqwHANiJU_mb36RNHRYXP8QgB1Yx3OSzmdpEwwHXoBEcCFVGdmqxG2laPeEqekNPyTB-AzVSNJ...
97 KB
97 KB
1158ms
1124ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiWhlJtKuqut1nJiSXcf5w9K1G5T6zfLNTs9CJkOPVNVlpd-9xb1oLSXHu5WlzvBlBkV7TYLdeqwHANiJU_mb36RNHRYXP8QgB1Yx3OSzmdpEwwHXoBEcCFVGdmqxG2laPeEqekNPyTB-AzVSNJlL4Ng0rfQfBXSeRwEAIFmWLcp_RCXdaHtFStLCor_Ic/s1600/nolimit%20city.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
1cf7f50f40a8868a0f1821986cf3a2c029251cc88b25bf9902fcc7205234c8e6
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v163"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
99560
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="nolimit city.gif"
GET
H3
200
NIU%20NIU.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjm0zcMEf3ajI0oVg1j59dOf7hO8C0Ovrx0wdRWfOtg27fXK6a7zx6d4mamh5RJZAeif-fvvjFoXoXvMgc6O0rDrdzdvEhSonB06pIrNFKQIQHLhhZPOsUmCqM_8pcceIcPYM5vYoUmtHOH2AjA...
66 KB
66 KB
938ms
904ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjm0zcMEf3ajI0oVg1j59dOf7hO8C0Ovrx0wdRWfOtg27fXK6a7zx6d4mamh5RJZAeif-fvvjFoXoXvMgc6O0rDrdzdvEhSonB06pIrNFKQIQHLhhZPOsUmCqM_8pcceIcPYM5vYoUmtHOH2AjAgh9JdW4ATmmDpPuI2EN22XNo8c_CTlM2cSTczb015YU/s1600/NIU%20NIU.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
b9c4dbdfba5601f8435783db29e4d6825ab5a0077c75077da62fa2959e787d38
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v165"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
67339
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="NIU NIU.gif"
GET
H3
200
monopoly.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgt3wWWIaLO-ab7CdckFJx4rcW35GaKgIpkPjgJWQ47leJfJZJ1fzJW88gBZVckCCl-Bli5zNtdnR_pFEi8j4fnOyvxHDgJ2YE6IbbAt2UnqaK2DLoZjhwvu47QnO4FjWLJKBnrZfeZKM91ej4V...
75 KB
75 KB
1049ms
1015ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgt3wWWIaLO-ab7CdckFJx4rcW35GaKgIpkPjgJWQ47leJfJZJ1fzJW88gBZVckCCl-Bli5zNtdnR_pFEi8j4fnOyvxHDgJ2YE6IbbAt2UnqaK2DLoZjhwvu47QnO4FjWLJKBnrZfeZKM91ej4VP2A4MApe1lhzcEz9DrUTauWJuC1nWbYxrk1DBZbZrxA/s1600/monopoly.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
7a1f1a71a4f70ce28960a0f908e973b0581e7ec579bd2dd317ba8e57c4ffaad0
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v163"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
76641
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="monopoly.gif"
GET
H3
200
mcro%20gaming.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjck2uh_vu3K1wbxtwH5j6ZDfAI3ozWmsoBrHqV7uFevvTVihTv8cuUxOtffbEewsK4gJX8y6-LNQAYhJc17sdjJyBKSGOspKAFXA9YoARPZ-VItrJ1bZ6ywIbo59kDut4O6EhFZ_ygQvPrU4ib...
95 KB
95 KB
786ms
753ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjck2uh_vu3K1wbxtwH5j6ZDfAI3ozWmsoBrHqV7uFevvTVihTv8cuUxOtffbEewsK4gJX8y6-LNQAYhJc17sdjJyBKSGOspKAFXA9YoARPZ-VItrJ1bZ6ywIbo59kDut4O6EhFZ_ygQvPrU4ibkGNQRIol99-zm4diTDLzvbA-OvJhHV5lEldPlQUcIlY/s1600/mcro%20gaming.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
8d8cc7cb23823ac85dc7eeba0e18de86d687fb6d2834c7cdbaef1aaec2171086
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v163"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
97651
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="mcro gaming.gif"
GET
H3
200
idn.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgYkPhGmS4o7_hZY6wES-qp0tfz605zuRlozlOfV8qs0rOT8WsuD76pUQ9WtxwnHi9J3nJf7GLLSPMOIBCgpFW8O5vVN7An4YPOvy8Evm2pl2MVAPhWVBrMh1WDjncvjSwqCoBpw4-Vue81aQWr...
75 KB
76 KB
884ms
850ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgYkPhGmS4o7_hZY6wES-qp0tfz605zuRlozlOfV8qs0rOT8WsuD76pUQ9WtxwnHi9J3nJf7GLLSPMOIBCgpFW8O5vVN7An4YPOvy8Evm2pl2MVAPhWVBrMh1WDjncvjSwqCoBpw4-Vue81aQWrMxpCHuQUkGE-xFQ3YyyjCfzYvGD2PRb_tvBNFxrtNgg/s1600/idn.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
ffb7cdfc96982a0186340d72bfd063b384437bbd34c8b5be3d5f409af0e16d91
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v164"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
77295
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="idn.gif"
GET
H3
200
IDN%204%20STAND.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiJ6j5yXduE2QbjmsqoN-UejWBlujCZxai9TXDaKc-1r4EBPc-TrrQAAf04NqHKn2Mym1UaTEFIw0CSvDy-rtkJzNdD5U7wLnnPZv7lgFXsXV4obU2GYaHHJ4cTaKCAd9KM6hiOLY9m49_B8ET9...
73 KB
73 KB
943ms
909ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiJ6j5yXduE2QbjmsqoN-UejWBlujCZxai9TXDaKc-1r4EBPc-TrrQAAf04NqHKn2Mym1UaTEFIw0CSvDy-rtkJzNdD5U7wLnnPZv7lgFXsXV4obU2GYaHHJ4cTaKCAd9KM6hiOLY9m49_B8ET96mgxYGFO4QFyAGOIIFqXVhVsoxEDcEPBvLUFMUt5s1E/s1600/IDN%204%20STAND.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
87d23728128b2b6f2af147c7c3c7e155d8a983a6ac7484303539a8c08028d847
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v164"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
74959
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="IDN 4 STAND.gif"
GET
H3
200
habanero.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEg6917iSWareXfCgv_Mg_4AW5eNk9v6xTBBdzrATQLL9Q-2wd7xOQEhRaR5jknPlwN0pEKZxhaT4vQ-_3Oi8C3XUXJbEmexFZtfVKJzdxxsGgOHoRqc4ByClNKXy2YLCFzcnjigC79weKExx20l...
98 KB
98 KB
961ms
928ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEg6917iSWareXfCgv_Mg_4AW5eNk9v6xTBBdzrATQLL9Q-2wd7xOQEhRaR5jknPlwN0pEKZxhaT4vQ-_3Oi8C3XUXJbEmexFZtfVKJzdxxsGgOHoRqc4ByClNKXy2YLCFzcnjigC79weKExx20ln7CAO3qDGLzXiB6bCer1FMkRZ8izoshnbRwxyiyI73I/s1600/habanero.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
6e173c68d135f300595874b5116db86cdebf11d35d5a1b26dd1eb517190e6896
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v165"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
100242
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="habanero.gif"
GET
H3
200
HEAD%20TAIL.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEg0EliWne032C7HlVYSf2qKRrWLA-3jhEWhuDi8OToGIUZt7wbeQNU-fozyrCPm0vhpbhLeng5MM-M0_g9pSTd9fw9xd-e01MSkryBgqgb_FT-25X-P7WAKUdX8MtF6U1JfNkBeZBU-FNdoGKao...
67 KB
67 KB
1180ms
1147ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEg0EliWne032C7HlVYSf2qKRrWLA-3jhEWhuDi8OToGIUZt7wbeQNU-fozyrCPm0vhpbhLeng5MM-M0_g9pSTd9fw9xd-e01MSkryBgqgb_FT-25X-P7WAKUdX8MtF6U1JfNkBeZBU-FNdoGKaoT-EfILhE1xBjFhW0tvFuL1ky_p6PbqBNeEG_eVmsyMk/s1600/HEAD%20TAIL.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
d4254882a1d386be367b1fce78e596f295a4d3739e31e1fb57537b862f9d1710
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v165"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
68851
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="HEAD TAIL.gif"
GET
H3
200
12D%20THUNDER.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEj_xsN7FtmAf3BdlugI8-0siwiacGqfhpko13VOFgupZTtap5XGX_XqEzQH_yX-84F088YNcxPuscGpXfpG53Vh_lr6K0d3ZLl8j74i9EJYXorfDLBhLrKOutw9Tk5MyN57TP7gXbEgKbBEolOD...
78 KB
78 KB
1159ms
1125ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEj_xsN7FtmAf3BdlugI8-0siwiacGqfhpko13VOFgupZTtap5XGX_XqEzQH_yX-84F088YNcxPuscGpXfpG53Vh_lr6K0d3ZLl8j74i9EJYXorfDLBhLrKOutw9Tk5MyN57TP7gXbEgKbBEolODspiEgHlsEy6sNL157fZ1DDmRNex_mlnlCA1d3CScAGU/s1600/12D%20THUNDER.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
7a61b3be6a7e0f1d32640743dfc716b6cf753a7f5e8df400c5f9b89a6982daeb
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v163"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
80112
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="12D THUNDER.gif"
GET
H3
200
FANTAN.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgFVjf80ngGx_64t3YIfyFDV8vGYPMlqJPdxIOChTgnCZA5jmOUBr9leltpc3b5OiEFJem_nmnb9-7yL0eezg6IvD6et391X_jLeZEf0KEoyJ9VZA_hJ2K1OCotWQ51xwOLpjeVDfpxOMFLkZTD...
60 KB
60 KB
1130ms
1097ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgFVjf80ngGx_64t3YIfyFDV8vGYPMlqJPdxIOChTgnCZA5jmOUBr9leltpc3b5OiEFJem_nmnb9-7yL0eezg6IvD6et391X_jLeZEf0KEoyJ9VZA_hJ2K1OCotWQ51xwOLpjeVDfpxOMFLkZTDVETUcD1cdG56WtDqbmCaD7pfwV1XQ8ug1jderm455GU/s1600/FANTAN.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
98d0fd56a39f3d137dc1b2d799b66d7270d7aa843d3a6159d2846d16002c0cb1
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v163"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
61319
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="FANTAN.gif"
GET
H3
200
dragon%20tiger.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEipfOYz-5rra99l-J97WZNb-CBunqN94GaiAY1LwDvd7w2Td4MsvXgjsq7w0s41_8w1Bq9yo8JqGhlNSsRDIUXuCL_rvfda38wBUf0EMjbfoyYTPYqJ0cJvTLhVh0iKolSFcOPVeIbDa0pA64K1...
98 KB
98 KB
1095ms
1061ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEipfOYz-5rra99l-J97WZNb-CBunqN94GaiAY1LwDvd7w2Td4MsvXgjsq7w0s41_8w1Bq9yo8JqGhlNSsRDIUXuCL_rvfda38wBUf0EMjbfoyYTPYqJ0cJvTLhVh0iKolSFcOPVeIbDa0pA64K1d5Lx8zSOFqoed2l7ArxYPdE0Lm8_qADNULI70w7DC60/s1600/dragon%20tiger.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
9b5174294cba545cd6c711f8b6a614d2782f70b82668bfd0229fc91c250adf97
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v164"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
99893
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="dragon tiger.gif"
GET
H3
200
DUEL%20DICE.gif
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjCBLuts34mEaT786EzbuN3SAO5A1Z4Ckn-8oxW71rliFguUwyZbHthA_T5YebOHxiCjRpfES0o5vEnCv4Y3lVI9IsidVsCeGS-SI-nGTSv-fUkabaAar0A4r4NbMKbpYTUvNNSThtJO0SDXY9w...
67 KB
67 KB
948ms
915ms
Image
image/gif
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjCBLuts34mEaT786EzbuN3SAO5A1Z4Ckn-8oxW71rliFguUwyZbHthA_T5YebOHxiCjRpfES0o5vEnCv4Y3lVI9IsidVsCeGS-SI-nGTSv-fUkabaAar0A4r4NbMKbpYTUvNNSThtJO0SDXY9wLYKyLCTHC2DfhsoK5XGCi_JVKxGx__3tTy6spWUqd7M/s1600/DUEL%20DICE.gif
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
f32fb09e3994db82c4d5411fde68cf309d9e637b9a7bc02457192bf1cdc4e4f8
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v166"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
69017
date
Sat, 19 Jul 2025 20:33:18 GMT
x-xss-protection
0
content-type
image/gif
vary
Origin
server
fife
content-disposition
inline;filename="DUEL DICE.gif"
GET
H2
200
widgets.js Show response
platform.twitter.com/
91 KB
27 KB
77ms
15ms
Script
application/javascript
199.232.44.157
FASTLY
General
Full URL
https://platform.twitter.com/widgets.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/assets/js/style.js?v=1.0
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
199.232.44.157 Singapore, Singapore, ASN54113 (FASTLY, US),
Reverse DNS
Software
/
Resource Hash
173460e89e6a7244218badae2016f65c48a3eae9d400802273eeca18b07336f1

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

content-encoding
gzip
etag
"824beb891744db98ccbd3a456e59e0f7+gzip"
access-control-allow-methods
GET
x-cache
HIT, HIT
p3p
CP="CAO DSP LAW CURa ADMa DEVa TAIa PSAa PSDa IVAa IVDa OUR BUS IND UNI COM NAV INT"
date
Sat, 19 Jul 2025 20:33:17 GMT
last-modified
Mon, 11 Dec 2023 17:20:28 GMT
vary
Accept-Encoding
x-served-by
cache-iad-kcgs7200137-IAD, cache-qpg1253-QPG
content-type
application/javascript; charset=utf-8
cache-control
public, max-age=1800
tw-cdn
FT
accept-ranges
bytes
access-control-allow-origin
*
content-length
27597
x-amz-server-side-encryption
AES256
GET
H2
200
floating-icon Show response
qqtotokiwi.site/json/
66 B
928 B
71ms
37ms
Fetch
application/json
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/json/floating-icon
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/js/custom/floating_icons.min.js?v=1752957196
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
678b72a40035fb2e414d41e9c938856b7d831eb6f364a35369f56c239ab837ba

Request headers

X-CSRF-TOKEN
YgkBMWoSoN3Dl8es8Qo9rFX8BmcZSnAQz7oNRiY1
Referer
https://qqtotokiwi.site/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Content-Type
application/json

Response headers

cache-control
no-cache, private
content-encoding
gzip
cf-cache-status
DYNAMIC
age
0
cf-ray
961cfe34e9553e06-SIN
accept-ranges
bytes
x-cache
MISS
content-length
82
date
Sat, 19 Jul 2025 20:33:17 GMT
content-type
application/json
vary
Accept-Encoding
x-cache-hits
0
server
cloudflare
GET
H2
200
main.js Show response
qqtotokiwi.site/cdn-cgi/challenge-platform/h/g/scripts/jsd/4d127ba5149d/ Frame 1D7B
Redirect Chain
  • https://qqtotokiwi.site/cdn-cgi/challenge-platform/scripts/jsd/main.js
  • https://qqtotokiwi.site/cdn-cgi/challenge-platform/h/g/scripts/jsd/4d127ba5149d/main.js?
10 KB
5 KB
14ms
10ms
Script
application/javascript
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/cdn-cgi/challenge-platform/h/g/scripts/jsd/4d127ba5149d/main.js?
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
31355131b072132880901e635c3d85f8db3b9994349b181fb747f8bfb24b706b
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer

Response headers

cache-control
max-age=14400, stale-if-error=10800, stale-while-revalidate=10800, public
content-encoding
gzip
x-content-type-options
nosniff
cf-ray
961cfe3589ad3e06-SIN
date
Sat, 19 Jul 2025 20:33:17 GMT
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
server
cloudflare

Redirect headers

cache-control
max-age=300, stale-if-error=10800, stale-while-revalidate=10800, public
location
/cdn-cgi/challenge-platform/h/g/scripts/jsd/4d127ba5149d/main.js?
cf-ray
961cfe35196b3e06-SIN
access-control-allow-origin
*
content-length
0
date
Sat, 19 Jul 2025 20:33:17 GMT
vary
Accept-Encoding
server
cloudflare
GET
H3
200
popup%20qqtoto.png
blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgqDL4CK6vJxSnh2sLYVyiNNKjAwF_UPkXK1nlhbCk6zX_RFyerw1YvWse-Y7rMcMO13VSszHDg50hf3Bpxc2H4FzHlDpqo1J5DfI118poqtY-jIZqARQr7LVcLqc0GVnGlwqkkAGGxIq9A1AW9...
536 KB
536 KB
296ms
268ms
Image
image/png
172.217.194.132
GOOGLE
General
Full URL
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgqDL4CK6vJxSnh2sLYVyiNNKjAwF_UPkXK1nlhbCk6zX_RFyerw1YvWse-Y7rMcMO13VSszHDg50hf3Bpxc2H4FzHlDpqo1J5DfI118poqtY-jIZqARQr7LVcLqc0GVnGlwqkkAGGxIq9A1AW972apAbmJoptCM2IbkknyTMbkGO5AXZ250YV46KXuAMM/s16000/popup%20qqtoto.png
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.217.194.132 , United States, ASN15169 (GOOGLE, US),
Reverse DNS
si-in-f132.1e100.net
Software
fife /
Resource Hash
16bc998d0c596a493cc28faf84708de5b6b0e15e854599c1f19d350299d3fc23
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-expose-headers
Content-Length
cache-control
public, max-age=86400, no-transform
etag
"v1c0"
x-content-type-options
nosniff
expires
Sun, 20 Jul 2025 20:33:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
548888
date
Sat, 19 Jul 2025 20:33:17 GMT
x-xss-protection
0
content-type
image/png
vary
Origin
server
fife
content-disposition
inline;filename="popup qqtoto.png"
GET
H2
200
get_configuration Show response
api.livechatinc.com/v3.5/customer/action/
5 KB
2 KB
261ms
249ms
Script
application/javascript
23.32.29.106
AKAMAI-ASN1 Akama...
General
Full URL
https://api.livechatinc.com/v3.5/customer/action/get_configuration?organization_id=9f4cf5ff-55c6-4c3d-a633-74ba3c34a52b&version=993.0.2.60.159.246.8.2.3.1.3.5.3&x-region=us-south1&group_id=0&jsonp=__lc_static_config
Requested by
Host: cdn.livechatinc.com
URL: https://cdn.livechatinc.com/tracking.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
23.32.29.106 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a23-32-29-106.deploy.static.akamaitechnologies.com
Software
/
Resource Hash
bf58fefb87f7b329edb0489d7ab7820932d2037655c9dbab7ee89b68cd077ace

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cache-control
public, max-age=600
content-encoding
gzip
cross-origin-resource-policy
cross-origin
expires
Sat, 19 Jul 2025 20:43:17 GMT
content-length
1835
date
Sat, 19 Jul 2025 20:33:17 GMT
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
GET
H2
200
widget_iframe.2f70fb173b9000da126c79afe2098f02.html Show response
platform.twitter.com/widgets/ Frame 05D0
319 KB
103 KB
16ms
4ms
Document
text/html
199.232.44.157
FASTLY
General
Full URL
https://platform.twitter.com/widgets/widget_iframe.2f70fb173b9000da126c79afe2098f02.html?origin=https%3A%2F%2Fqqtotokiwi.site
Requested by
Host: platform.twitter.com
URL: https://platform.twitter.com/widgets.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
199.232.44.157 Singapore, Singapore, ASN54113 (FASTLY, US),
Reverse DNS
Software
/
Resource Hash
70c00445d6632039ed99af760731daf3bf60eb12061863ee61e2cd7276a54d18

Request headers

Referer
https://qqtotokiwi.site/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36

Response headers

accept-ranges
bytes
access-control-allow-methods
GET
access-control-allow-origin
*
cache-control
public, max-age=315360000
content-encoding
gzip
content-length
105429
content-type
text/html; charset=utf-8
date
Sat, 19 Jul 2025 20:33:17 GMT
etag
"81267302efdfb3e4524a22631a8fc99e+gzip"
last-modified
Mon, 11 Dec 2023 17:19:49 GMT
p3p
CP="CAO DSP LAW CURa ADMa DEVa TAIa PSAa PSDa IVAa IVDa OUR BUS IND UNI COM NAV INT"
tw-cdn
FT
vary
Accept-Encoding
x-amz-server-side-encryption
AES256
x-cache
HIT, HIT
x-served-by
cache-iad-kiad7000164-IAD, cache-qpg1269-QPG
POST
H2
200
961cfe2c2c3a3e06 Show response
qqtotokiwi.site/cdn-cgi/challenge-platform/h/g/jsd/r/0.7973330452600781:1752955988:RC9oQuS_V_ahL_6iJPkSSCm-5ET0jugYf67YjUjD3Qo/ Frame 1D7B
0
391 B
23ms
16ms
XHR
text/plain
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/cdn-cgi/challenge-platform/h/g/jsd/r/0.7973330452600781:1752955988:RC9oQuS_V_ahL_6iJPkSSCm-5ET0jugYf67YjUjD3Qo/961cfe2c2c3a3e06
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/cdn-cgi/challenge-platform/scripts/jsd/main.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Content-Type
text/plain;charset=UTF-8
Referer

Response headers

cf-ray
961cfe374ace3e06-SIN
content-length
0
date
Sat, 19 Jul 2025 20:33:17 GMT
content-type
text/plain; charset=UTF-8
server
cloudflare
GET
H2
200
settings Show response
syndication.twitter.com/ Frame 05D0
870 B
956 B
245ms
226ms
Fetch
application/json
162.159.140.229
CLOUDFLARENET
General
Full URL
https://syndication.twitter.com/settings?session_id=ef79eaffa76224f00b20fe347a3843b22cbf690e
Requested by
Host: platform.twitter.com
URL: https://platform.twitter.com/widgets/widget_iframe.2f70fb173b9000da126c79afe2098f02.html?origin=https%3A%2F%2Fqqtotokiwi.site
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
162.159.140.229 , Ascension Island, ASN13335 (CLOUDFLARENET, US),
Reverse DNS
Software
cloudflare tsa_p /
Resource Hash
8ec44a4b321f5115d8760f193298585d8b28a26dd3190d0a3690b9e09a489a94
Security Headers
Name Value
Strict-Transport-Security max-age=631138519; includeSubdomains

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://platform.twitter.com/

Response headers

x-transaction-id
803187ef75f586e7
x-connection-hash
5f60dcc2a142b02ee27f658c0b8ea9b4e76ff56d30e35a3719aac941c8eab072
content-encoding
gzip
cf-cache-status
DYNAMIC
x-response-time
5
date
Sat, 19 Jul 2025 20:33:18 GMT
content-type
application/json; charset=utf-8
perf
7402827104
vary
Origin, accept-encoding
last-modified
Sat, 19 Jul 2025 20:33:18 GMT
strict-transport-security
max-age=631138519; includeSubdomains
cache-control
must-revalidate, max-age=600
access-control-allow-credentials
true
cf-ray
961cfe37fa5881bf-SIN
access-control-allow-origin
https://platform.twitter.com
content-length
338
server
cloudflare tsa_p
GET
H/1.1
200
OK
open_chat Show response
secure.livechatinc.com/customer/action/ Frame EEBA
2 KB
990 B
648ms
625ms
Document
text/html
125.56.219.3
AKAMAI-ASN1 Akama...
General
Full URL
https://secure.livechatinc.com/customer/action/open_chat?license_id=15132858&group=0&embedded=1&widget_version=3&unique_groups=0&organizationId=9f4cf5ff-55c6-4c3d-a633-74ba3c34a52b&use_parent_storage=1&x-region=us-south1
Requested by
Host: cdn.livechatinc.com
URL: https://cdn.livechatinc.com/tracking.js
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_256_GCM
Server
125.56.219.3 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a125-56-219-3.deploy.static.akamaitechnologies.com
Software
/
Resource Hash
68e6fc98225baa9cb03f1bd4875cdf6af3dde125fd0288838891474b3551416b

Request headers

Referer
https://qqtotokiwi.site/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36

Response headers

Connection
keep-alive
Content-Encoding
gzip
Content-Length
758
Content-Type
text/html; charset=utf-8
Date
Sat, 19 Jul 2025 20:33:18 GMT
Vary
Accept-Encoding
cross-origin-resource-policy
cross-origin
GET
H2
200
get_localization Show response
api.livechatinc.com/v3.5/customer/action/
13 KB
5 KB
262ms
260ms
Script
application/javascript
23.32.29.106
AKAMAI-ASN1 Akama...
General
Full URL
https://api.livechatinc.com/v3.5/customer/action/get_localization?organization_id=9f4cf5ff-55c6-4c3d-a633-74ba3c34a52b&version=e72cb3bc3c47bc3d85e9a0bafe141ee5_571a4ad6322abb18003df5a516922e3f&language=id&x-region=us-south1&group_id=0&jsonp=__lc_localization
Requested by
Host: cdn.livechatinc.com
URL: https://cdn.livechatinc.com/tracking.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
23.32.29.106 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a23-32-29-106.deploy.static.akamaitechnologies.com
Software
/
Resource Hash
d2eef1bcb32f4a121cb14ee6890dd34cc8aa9738e456cf8358d06d137c508402

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cache-control
public, max-age=600
content-encoding
gzip
cross-origin-resource-policy
cross-origin
expires
Sat, 19 Jul 2025 20:43:18 GMT
content-length
4501
date
Sat, 19 Jul 2025 20:33:18 GMT
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
GET
H2
200
b4c688399c01f0bd671b45403ba2c1ac.png
i.gyazo.com/
2 KB
2 KB
128ms
64ms
Image
image/png
104.18.24.163
CLOUDFLARENET
General
Full URL
https://i.gyazo.com/b4c688399c01f0bd671b45403ba2c1ac.png
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.18.24.163 , Ascension Island, ASN13335 (CLOUDFLARENET, US),
Reverse DNS
Software
cloudflare /
Resource Hash
f903a7866ddb2a49d1f4a97bae6f04d4996f5b22bc85ad57ae74bd8911245322

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cf-cache-status
HIT
etag
"b4c6"
age
504133
expires
Sun, 19 Jul 2026 20:33:18 GMT
date
Sat, 19 Jul 2025 20:33:18 GMT
content-type
image/png
vary
Accept-Encoding
cache-control
public, max-age=31536000
x-cache-level
ZS
access-control-allow-credentials
true
via
1.1 google
cf-ray
961cfe3a3c598de9-SIN
accept-ranges
bytes
access-control-allow-origin
https://gyazo.com
content-length
1773
server
cloudflare
GET
H2
200
livechat.YgrBLwQa.js Show response
cdn.livechatinc.com/widget/static/js/ Frame EEBA
463 B
1 KB
16ms
4ms
Script
application/javascript
184.51.6.218
AKAMAI-ASN1 Akama...
General
Full URL
https://cdn.livechatinc.com/widget/static/js/livechat.YgrBLwQa.js
Requested by
Host: secure.livechatinc.com
URL: https://secure.livechatinc.com/customer/action/open_chat?license_id=15132858&group=0&embedded=1&widget_version=3&unique_groups=0&organizationId=9f4cf5ff-55c6-4c3d-a633-74ba3c34a52b&use_parent_storage=1&x-region=us-south1
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
184.51.6.218 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a184-51-6-218.deploy.static.akamaitechnologies.com
Software
UploadServer /
Resource Hash
1c34b1ce3038b7de035f61ca1ea0908230c2e3a8f6b01b261802034f3e8605da

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Origin
https://secure.livechatinc.com
Referer
https://secure.livechatinc.com/

Response headers

x-goog-metageneration
1
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=odMRrA==, md5=Fo/a8iMMOzayqVXo6RJsGg==
etag
"168fdaf2230c3b36b2a955e8e9126c1a"
x-goog-stored-content-encoding
identity
expires
Sun, 19 Jul 2026 20:33:19 GMT
x-goog-stored-content-length
463
date
Sat, 19 Jul 2025 20:33:19 GMT
last-modified
Wed, 16 Jul 2025 07:36:13 GMT
vary
Accept-Encoding
content-type
application/javascript; charset=utf-8
x-guploader-uploadid
ABgVH88xuKToWtXM4gAUpZm4xrc5tIt6LXzd-yC_DTvgh_6zh_MwlbX0qcOMd8yP7u5egUIJHUoEzryI7NNDKg
cache-control
public, max-age=31536000
x-goog-storage-class
STANDARD
access-control-allow-origin
*
x-goog-generation
1752651373526376
content-length
463
server
UploadServer
GET
H2
200
0.CwqP73vu.chunk.js Show response
cdn.livechatinc.com/widget/static/js/ Frame EEBA
67 KB
22 KB
19ms
3ms
Script
application/javascript
184.51.6.218
AKAMAI-ASN1 Akama...
General
Full URL
https://cdn.livechatinc.com/widget/static/js/0.CwqP73vu.chunk.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
184.51.6.218 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a184-51-6-218.deploy.static.akamaitechnologies.com
Software
UploadServer /
Resource Hash
06de4fe93f009e650e7afeb27516d603019d8721cc0e236eff8a06ef4abf0520

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Origin
https://secure.livechatinc.com
Referer
https://cdn.livechatinc.com/widget/static/js/livechat.YgrBLwQa.js

Response headers

x-goog-metageneration
1
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=8XStcw==, md5=Oc9hyk+neGdl+XAIkFVihg==
content-encoding
br
x-goog-stored-content-encoding
identity
expires
Sun, 19 Jul 2026 20:33:19 GMT
x-goog-stored-content-length
68132
date
Sat, 19 Jul 2025 20:33:19 GMT
last-modified
Wed, 16 Jul 2025 07:36:13 GMT
content-type
application/javascript; charset=utf-8
x-guploader-uploadid
ABgVH89IMFm-51widUpLyhpodzCX3MnJAuBurm9efcrehxWF7nXD1b1uv9R1YngeybMoSv5C2otpdRE
cache-control
public, max-age=31536000
x-goog-storage-class
STANDARD
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1752651373454917
content-length
21773
server
UploadServer
GET
H2
200
1.DkDUYs7W.chunk.js Show response
cdn.livechatinc.com/widget/static/js/ Frame EEBA
51 KB
19 KB
21ms
5ms
Script
application/javascript
184.51.6.218
AKAMAI-ASN1 Akama...
General
Full URL
https://cdn.livechatinc.com/widget/static/js/1.DkDUYs7W.chunk.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
184.51.6.218 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a184-51-6-218.deploy.static.akamaitechnologies.com
Software
UploadServer /
Resource Hash
448148caad199e5db2c080922b6e144247efa3afdb52c0ab682cf9a5c729d352

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Origin
https://secure.livechatinc.com
Referer
https://cdn.livechatinc.com/widget/static/js/livechat.YgrBLwQa.js

Response headers

x-goog-metageneration
1
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=gLCQvg==, md5=2nQIHwd2gi+9Vj9PxAhXNg==
content-encoding
br
x-goog-stored-content-encoding
identity
expires
Sun, 19 Jul 2026 20:33:19 GMT
x-goog-stored-content-length
52395
date
Sat, 19 Jul 2025 20:33:19 GMT
last-modified
Wed, 16 Jul 2025 07:36:13 GMT
content-type
application/javascript; charset=utf-8
x-guploader-uploadid
ABgVH89-CxZlb-oBCDRGxnx4qhU9NZCrCGnNM7BxJf2dERgRfuz72b4WsLyT_OPlwJJ8Ekp2h9pPppCwj7yw9w
cache-control
public, max-age=31536000
x-goog-storage-class
STANDARD
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1752651373451942
content-length
18969
server
UploadServer
GET
H2
200
2.1K4W5B1m.chunk.js Show response
cdn.livechatinc.com/widget/static/js/ Frame EEBA
352 KB
103 KB
23ms
8ms
Script
application/javascript
184.51.6.218
AKAMAI-ASN1 Akama...
General
Full URL
https://cdn.livechatinc.com/widget/static/js/2.1K4W5B1m.chunk.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
184.51.6.218 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a184-51-6-218.deploy.static.akamaitechnologies.com
Software
UploadServer /
Resource Hash
432c6730124baa271718e80f940c4c680522619658de6a581931348d43e06b6e

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Origin
https://secure.livechatinc.com
Referer
https://cdn.livechatinc.com/widget/static/js/livechat.YgrBLwQa.js

Response headers

x-goog-metageneration
1
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=buYzYA==, md5=DyHyzf3BYsSis6ovlacKBg==
content-encoding
br
x-goog-stored-content-encoding
identity
expires
Sun, 19 Jul 2026 20:33:19 GMT
x-goog-stored-content-length
360060
date
Sat, 19 Jul 2025 20:33:19 GMT
last-modified
Wed, 16 Jul 2025 07:36:13 GMT
content-type
application/javascript; charset=utf-8
x-guploader-uploadid
ABgVH89El58nlG5DBlMB8zmBfMrxMCYRaLOZbfxJGHZjlW8LKoiL_76WrO31XobNhqA9_lJ2b6UtaWUjB_JPtg
cache-control
public, max-age=31536000
x-goog-storage-class
STANDARD
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1752651373547924
content-length
104515
server
UploadServer
GET
H2
200
3.DGuSL2Mg.chunk.js Show response
cdn.livechatinc.com/widget/static/js/ Frame EEBA
190 KB
61 KB
25ms
10ms
Script
application/javascript
184.51.6.218
AKAMAI-ASN1 Akama...
General
Full URL
https://cdn.livechatinc.com/widget/static/js/3.DGuSL2Mg.chunk.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
184.51.6.218 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a184-51-6-218.deploy.static.akamaitechnologies.com
Software
UploadServer /
Resource Hash
a6f8e423ac60837d470b983a555446cba672ae4ed02b90880e7869d79088335d

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Origin
https://secure.livechatinc.com
Referer
https://cdn.livechatinc.com/widget/static/js/livechat.YgrBLwQa.js

Response headers

x-goog-metageneration
1
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=ymNIEw==, md5=u8XUQBr/zWe+gj3N72NmvA==
content-encoding
br
x-goog-stored-content-encoding
identity
expires
Sun, 19 Jul 2026 20:33:19 GMT
x-goog-stored-content-length
194893
date
Sat, 19 Jul 2025 20:33:19 GMT
last-modified
Wed, 16 Jul 2025 07:36:13 GMT
content-type
application/javascript; charset=utf-8
x-guploader-uploadid
ABgVH8-mKWoiNFhnlqRZ3HQyF1Cx5R48QHX048pQPogWi0Dk_9vfTnBQ3pwLJGMjYr9Gp_rzJ17Ax5s
cache-control
public, max-age=31536000
x-goog-storage-class
STANDARD
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1752651373520161
content-length
61954
server
UploadServer
GET
H2
200
4.C_rgEAoe.chunk.js Show response
cdn.livechatinc.com/widget/static/js/ Frame EEBA
193 B
756 B
21ms
7ms
Script
application/javascript
184.51.6.218
AKAMAI-ASN1 Akama...
General
Full URL
https://cdn.livechatinc.com/widget/static/js/4.C_rgEAoe.chunk.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
184.51.6.218 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a184-51-6-218.deploy.static.akamaitechnologies.com
Software
UploadServer /
Resource Hash
6e148df31d721a0ff08563f2d676751786e01418c86ee54ee8f0e88aa46ae26a

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Origin
https://secure.livechatinc.com
Referer
https://cdn.livechatinc.com/widget/static/js/livechat.YgrBLwQa.js

Response headers

x-goog-metageneration
1
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=C03sAA==, md5=F3E3bcB9pIs/AzOdhtV7ew==
etag
"1771376dc07da48b3f03339d86d57b7b"
x-goog-stored-content-encoding
identity
expires
Sun, 19 Jul 2026 20:33:19 GMT
x-goog-stored-content-length
193
date
Sat, 19 Jul 2025 20:33:19 GMT
last-modified
Wed, 16 Jul 2025 07:36:13 GMT
content-type
application/javascript; charset=utf-8
x-guploader-uploadid
ABgVH88ufjXMvty0Imxd9PIn39h4C4Uh4lRCsd6yO8P05Q4kwoSnh1ikZQ9GeOmdQ-kOSQjPRcG3DzaUlfWNWQ
cache-control
public, max-age=31536000
x-goog-storage-class
STANDARD
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1752651373494306
content-length
193
server
UploadServer
GET
H2
200
5.D_uKc_ak.chunk.js Show response
cdn.livechatinc.com/widget/static/js/ Frame EEBA
134 KB
43 KB
27ms
13ms
Script
application/javascript
184.51.6.218
AKAMAI-ASN1 Akama...
General
Full URL
https://cdn.livechatinc.com/widget/static/js/5.D_uKc_ak.chunk.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
184.51.6.218 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a184-51-6-218.deploy.static.akamaitechnologies.com
Software
UploadServer /
Resource Hash
cc9af994a65e2deac1f388408504e6a4059652a5c652bcbfd0898731b9153be0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Origin
https://secure.livechatinc.com
Referer
https://cdn.livechatinc.com/widget/static/js/livechat.YgrBLwQa.js

Response headers

x-goog-metageneration
1
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=o9ILpQ==, md5=xY2zPwTLrikJbeVq+HwyhA==
content-encoding
br
x-goog-stored-content-encoding
identity
expires
Sun, 19 Jul 2026 20:33:19 GMT
x-goog-stored-content-length
137495
date
Sat, 19 Jul 2025 20:33:19 GMT
last-modified
Wed, 16 Jul 2025 07:36:13 GMT
content-type
application/javascript; charset=utf-8
x-guploader-uploadid
ABgVH889tqdBiUbAtnmSCYWhUId7GXJCPIvLggY5L_ALVrJgS0kiGY-u5rHgrVPr5oCXX9XX1Sas4fg
cache-control
public, max-age=31536000
x-goog-storage-class
STANDARD
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1752651373533284
content-length
43283
server
UploadServer
GET
H2
200
6.D_CKFAbE.chunk.js Show response
cdn.livechatinc.com/widget/static/js/ Frame EEBA
782 B
1 KB
30ms
17ms
Script
application/javascript
184.51.6.218
AKAMAI-ASN1 Akama...
General
Full URL
https://cdn.livechatinc.com/widget/static/js/6.D_CKFAbE.chunk.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
184.51.6.218 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a184-51-6-218.deploy.static.akamaitechnologies.com
Software
UploadServer /
Resource Hash
62ceb8a88b98bbe24a3b9fd8d65f58988e3b424bdb754e8d3effcc2d18e6d6c2

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Origin
https://secure.livechatinc.com
Referer
https://cdn.livechatinc.com/widget/static/js/livechat.YgrBLwQa.js

Response headers

x-goog-metageneration
1
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=XQhoqw==, md5=p7wTQ/uE2j8nYWzI2O3M4A==
etag
"a7bc1343fb84da3f27616cc8d8edcce0"
x-goog-stored-content-encoding
identity
expires
Sun, 19 Jul 2026 20:33:19 GMT
x-goog-stored-content-length
782
date
Sat, 19 Jul 2025 20:33:19 GMT
last-modified
Wed, 16 Jul 2025 07:36:13 GMT
vary
Accept-Encoding
content-type
application/javascript; charset=utf-8
x-guploader-uploadid
ABgVH8_voBQrtZ1t_6ncHB8iVj-sLhs5vrgJNQaryN2tSVNTKJpaFld4Zwtvgg8XaRm3B_ClFN5yWiQ
cache-control
public, max-age=31536000
x-goog-storage-class
STANDARD
access-control-allow-origin
*
x-goog-generation
1752651373498236
content-length
782
server
UploadServer
GET
H2
200
7.xhyEK0_l.chunk.js Show response
cdn.livechatinc.com/widget/static/js/ Frame EEBA
74 B
633 B
29ms
15ms
Script
application/javascript
184.51.6.218
AKAMAI-ASN1 Akama...
General
Full URL
https://cdn.livechatinc.com/widget/static/js/7.xhyEK0_l.chunk.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
184.51.6.218 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a184-51-6-218.deploy.static.akamaitechnologies.com
Software
UploadServer /
Resource Hash
af2012b0cdfa449f186df2f8dc9b3e64b48b8c5c630cc8d3c4df61973499e7c4

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Origin
https://secure.livechatinc.com
Referer
https://cdn.livechatinc.com/widget/static/js/livechat.YgrBLwQa.js

Response headers

x-goog-metageneration
1
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=pjIEnA==, md5=yWo5Rg0rCpJAmyuS89qI+Q==
etag
"c96a39460d2b0a92409b2b92f3da88f9"
x-goog-stored-content-encoding
identity
expires
Sun, 19 Jul 2026 20:33:19 GMT
x-goog-stored-content-length
74
date
Sat, 19 Jul 2025 20:33:19 GMT
last-modified
Wed, 16 Jul 2025 07:36:13 GMT
vary
Accept-Encoding
content-type
application/javascript; charset=utf-8
x-guploader-uploadid
ABgVH885aMdr309WXGbOSzYzWtISBZ32bvymFaEW3_kmHNTzfMheAoZydSP2M-N4Rsh3GkWt
cache-control
public, max-age=31536000
x-goog-storage-class
STANDARD
access-control-allow-origin
*
x-goog-generation
1752651373501993
content-length
74
server
UploadServer
GET
H2
200
8.qYTqns9Q.chunk.js Show response
cdn.livechatinc.com/widget/static/js/ Frame EEBA
40 B
609 B
29ms
16ms
Script
application/javascript
184.51.6.218
AKAMAI-ASN1 Akama...
General
Full URL
https://cdn.livechatinc.com/widget/static/js/8.qYTqns9Q.chunk.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
184.51.6.218 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a184-51-6-218.deploy.static.akamaitechnologies.com
Software
UploadServer /
Resource Hash
80353503e48ebf6c2ae9f70184d3e758f64bacf48afe147e039df807509200cb

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Origin
https://secure.livechatinc.com
Referer
https://cdn.livechatinc.com/widget/static/js/livechat.YgrBLwQa.js

Response headers

x-goog-metageneration
1
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=jQQqwg==, md5=1UHOLXVEArgzzGW3bq6ixg==
etag
"d541ce2d754402b833cc65b76eaea2c6"
x-goog-stored-content-encoding
identity
expires
Sun, 19 Jul 2026 20:33:19 GMT
x-goog-stored-content-length
40
date
Sat, 19 Jul 2025 20:33:19 GMT
last-modified
Wed, 16 Jul 2025 07:36:13 GMT
vary
Accept-Encoding
content-type
application/javascript; charset=utf-8
x-guploader-uploadid
ABgVH89r2eTbcDbWZbbjNjhi3ldb-UH8SlxKnD6RhMcE5-jg9uqaFvArRX2-ryGP21GbcEtPNPH46tR6ILkBuA
cache-control
public, max-age=31536000
x-goog-storage-class
STANDARD
access-control-allow-origin
*
x-goog-generation
1752651373507668
content-length
40
server
UploadServer
GET
H2
200
9.CXyc5yX6.chunk.js Show response
cdn.livechatinc.com/widget/static/js/ Frame EEBA
21 KB
7 KB
8ms
4ms
Script
application/javascript
184.51.6.218
AKAMAI-ASN1 Akama...
General
Full URL
https://cdn.livechatinc.com/widget/static/js/9.CXyc5yX6.chunk.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
184.51.6.218 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a184-51-6-218.deploy.static.akamaitechnologies.com
Software
UploadServer /
Resource Hash
04f53e275240ef1c293ba4a40873657150254683cca3b8129ea63b98dbaf541e

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Origin
https://secure.livechatinc.com
Referer
https://cdn.livechatinc.com/widget/static/js/livechat.YgrBLwQa.js

Response headers

x-goog-metageneration
1
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=OHY+wA==, md5=Y4132tNU1iEJFFoesY9qnA==
content-encoding
br
x-goog-stored-content-encoding
identity
expires
Sun, 19 Jul 2026 20:33:19 GMT
x-goog-stored-content-length
21042
date
Sat, 19 Jul 2025 20:33:19 GMT
last-modified
Wed, 16 Jul 2025 07:36:13 GMT
content-type
application/javascript; charset=utf-8
x-guploader-uploadid
ABgVH89PyC6CEnso0v6-QbtD73Oi_bxSSBnelbi2rqD8oKg3PXL3D8TN8LAt60vAbGpkda-zxStu1A
cache-control
public, max-age=31536000
x-goog-storage-class
STANDARD
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1752651373502920
content-length
6669
server
UploadServer
GET
H2
200
10.DOCsjrrg.chunk.js Show response
cdn.livechatinc.com/widget/static/js/ Frame EEBA
307 B
878 B
21ms
19ms
Script
application/javascript
184.51.6.218
AKAMAI-ASN1 Akama...
General
Full URL
https://cdn.livechatinc.com/widget/static/js/10.DOCsjrrg.chunk.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
184.51.6.218 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a184-51-6-218.deploy.static.akamaitechnologies.com
Software
UploadServer /
Resource Hash
f4442ae282d43f6efc118b7903e05b3cf992507195239ddae6143f8b91342731

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Origin
https://secure.livechatinc.com
Referer
https://cdn.livechatinc.com/widget/static/js/livechat.YgrBLwQa.js

Response headers

x-goog-metageneration
1
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=fPxBxA==, md5=lQjOfaAm+HU6l8Df6dtWSg==
etag
"9508ce7da026f8753a97c0dfe9db564a"
x-goog-stored-content-encoding
identity
expires
Sun, 19 Jul 2026 20:33:19 GMT
x-goog-stored-content-length
307
date
Sat, 19 Jul 2025 20:33:19 GMT
last-modified
Wed, 16 Jul 2025 07:36:13 GMT
vary
Accept-Encoding
content-type
application/javascript; charset=utf-8
x-guploader-uploadid
ABgVH8-qu5O6t0KRvT6QdOuzT6maJ2Ogs53OWgexid1am0CCE_96VUg7BQuwnKQ3KgRtfYoxOEuLjOqr6AKb6A
cache-control
public, max-age=31536000
x-goog-storage-class
STANDARD
access-control-allow-origin
*
x-goog-generation
1752651373439456
content-length
307
server
UploadServer
GET
H2
200
11.Gv78iMd6.chunk.js Show response
cdn.livechatinc.com/widget/static/js/ Frame EEBA
240 B
802 B
22ms
20ms
Script
application/javascript
184.51.6.218
AKAMAI-ASN1 Akama...
General
Full URL
https://cdn.livechatinc.com/widget/static/js/11.Gv78iMd6.chunk.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
184.51.6.218 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a184-51-6-218.deploy.static.akamaitechnologies.com
Software
UploadServer /
Resource Hash
d3b76fb03a7607b5da00fc0252be26fef8c76a0b68feb2ff19b439eeeab3f705

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Origin
https://secure.livechatinc.com
Referer
https://cdn.livechatinc.com/widget/static/js/livechat.YgrBLwQa.js

Response headers

x-goog-metageneration
1
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=1j+HPw==, md5=jslABcJcfgh0t7BI6pfcAA==
etag
"8ec94005c25c7e0874b7b048ea97dc00"
x-goog-stored-content-encoding
identity
expires
Sun, 19 Jul 2026 20:33:19 GMT
x-goog-stored-content-length
240
date
Sat, 19 Jul 2025 20:33:19 GMT
last-modified
Wed, 16 Jul 2025 07:36:13 GMT
vary
Accept-Encoding
content-type
application/javascript; charset=utf-8
x-guploader-uploadid
ABgVH8-Hzn96ZvDGhaKg51XIjM4nR8G7HGyzCvAr7zW0QpBpbMfrdHKVrW8PpEU_6As5KboJb3BgOv4
cache-control
public, max-age=31536000
x-goog-storage-class
STANDARD
access-control-allow-origin
*
x-goog-generation
1752651373458719
content-length
240
server
UploadServer
GET
H2
200
12.DJPUQwQu.chunk.js Show response
cdn.livechatinc.com/widget/static/js/ Frame EEBA
300 B
863 B
20ms
18ms
Script
application/javascript
184.51.6.218
AKAMAI-ASN1 Akama...
General
Full URL
https://cdn.livechatinc.com/widget/static/js/12.DJPUQwQu.chunk.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
184.51.6.218 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a184-51-6-218.deploy.static.akamaitechnologies.com
Software
UploadServer /
Resource Hash
fb8eb817d7251014c136b441bd4004fa6567908059013edbb938925f23b67ceb

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Origin
https://secure.livechatinc.com
Referer
https://cdn.livechatinc.com/widget/static/js/livechat.YgrBLwQa.js

Response headers

x-goog-metageneration
1
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=IuJCUg==, md5=ZAyqtSEAoenf5hiq63mDjw==
etag
"640caab52100a1e9dfe618aaeb79838f"
x-goog-stored-content-encoding
identity
expires
Sun, 19 Jul 2026 20:33:19 GMT
x-goog-stored-content-length
300
date
Sat, 19 Jul 2025 20:33:19 GMT
last-modified
Wed, 16 Jul 2025 07:36:13 GMT
vary
Accept-Encoding
content-type
application/javascript; charset=utf-8
x-guploader-uploadid
ABgVH8_p-nN0Odex9HVxDD1wIyKN7Vry22IbNXJzdIVQrarp1loapL4NKJLdi6zYh5HxUO3YzMHQ0yk
cache-control
public, max-age=31536000
x-goog-storage-class
STANDARD
access-control-allow-origin
*
x-goog-generation
1752651373445543
content-length
300
server
UploadServer
GET
H2
200
13.Du4z9uvj.chunk.js Show response
cdn.livechatinc.com/widget/static/js/ Frame EEBA
231 B
799 B
23ms
21ms
Script
application/javascript
184.51.6.218
AKAMAI-ASN1 Akama...
General
Full URL
https://cdn.livechatinc.com/widget/static/js/13.Du4z9uvj.chunk.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
184.51.6.218 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a184-51-6-218.deploy.static.akamaitechnologies.com
Software
UploadServer /
Resource Hash
bc125921b5e4dde1c19d4fbc0a6ef3ea616eee9577822c96b29789b7f69ba5fd

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Origin
https://secure.livechatinc.com
Referer
https://cdn.livechatinc.com/widget/static/js/livechat.YgrBLwQa.js

Response headers

x-goog-metageneration
1
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=aPUdaA==, md5=x3xwyFcGlNXiBVNxGm0bKA==
etag
"c77c70c8570694d5e20553711a6d1b28"
x-goog-stored-content-encoding
identity
expires
Sun, 19 Jul 2026 20:33:19 GMT
x-goog-stored-content-length
231
date
Sat, 19 Jul 2025 20:33:19 GMT
last-modified
Wed, 16 Jul 2025 07:36:13 GMT
vary
Accept-Encoding
content-type
application/javascript; charset=utf-8
x-guploader-uploadid
ABgVH89ciCH8deOYXdMrT-zXkmghcOwFvzIY9qZshjxYSi7j0AKmgC1p8C68iLCWmyfAfyBJoOWbDhcQtQ3G-w
cache-control
public, max-age=31536000
x-goog-storage-class
STANDARD
access-control-allow-origin
*
x-goog-generation
1752651373439580
content-length
231
server
UploadServer
POST
H2
200
token Show response
accounts.livechatinc.com/v2/customer/ Frame EEBA
201 B
1 KB
228ms
207ms
XHR
application/json
96.17.96.8
AKAMAI-ASN1 Akama...
General
Full URL
https://accounts.livechatinc.com/v2/customer/token
Requested by
Host: cdn.livechatinc.com
URL: https://cdn.livechatinc.com/widget/static/js/3.DGuSL2Mg.chunk.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
96.17.96.8 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a96-17-96-8.deploy.static.akamaitechnologies.com
Software
/
Resource Hash
ceba2f1142d6a9fde6e9ce01cc9367428710b37d2e9faea839cc5c3d34966dfb
Security Headers
Name Value
Strict-Transport-Security max-age=86400 ; includeSubDomains

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Content-Type
text/plain;charset=UTF-8
Referer
https://secure.livechatinc.com/

Response headers

strict-transport-security
max-age=86400 ; includeSubDomains
cache-control
no-cache, no-store, max-age=0, must-revalidate
pragma
no-cache
access-control-allow-credentials
true
expires
Fri, 01 Jan 1990 00:00:00 GMT
access-control-allow-origin
https://secure.livechatinc.com
content-length
201
date
Sat, 19 Jul 2025 20:33:19 GMT
content-type
application/json
GET
H2
200
data Show response
qqtotokiwi.site/json/fetch/index/
22 KB
3 KB
45ms
44ms
Fetch
application/json
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/json/fetch/index/data
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/js/frontend/desktop/template_v1/before/index.js?v=c3syfye1yivoif3u4mel
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
21283e24743d7dcd1055c1caa8ef55a0d1200564029851e3b61af78cc44e68f5

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Content-Type
application/json
Referer
https://qqtotokiwi.site/

Response headers

cache-control
no-cache, private
content-encoding
gzip
cf-cache-status
DYNAMIC
age
0
cf-ray
961cfe40383f3e06-SIN
accept-ranges
bytes
x-cache
MISS
date
Sat, 19 Jul 2025 20:33:19 GMT
content-type
application/json
vary
Accept-Encoding
x-cache-hits
0
server
cloudflare
POST
H2
204
rum Show response
qqtotokiwi.site/cdn-cgi/
0
159 B
13ms
6ms
XHR
text/plain
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/cdn-cgi/rum?
Requested by
Host: static.cloudflareinsights.com
URL: https://static.cloudflareinsights.com/beacon.min.js/vcd15cbe7772f49c399c6a5babf22c1241717689176015
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options DENY

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
content-type
application/json
Referer
https://qqtotokiwi.site/

Response headers

access-control-max-age
86400
access-control-allow-credentials
true
access-control-allow-methods
POST,OPTIONS
x-content-type-options
nosniff
cf-ray
961cfe4188f33e06-SIN
access-control-allow-origin
https://qqtotokiwi.site
date
Sat, 19 Jul 2025 20:33:19 GMT
vary
Origin
server
cloudflare
x-frame-options
DENY
GET
H2
200
favicon.png
qqtotokiwi.site/assets/img/bsq/
2 KB
2 KB
18ms
18ms
Other
image/png
92.243.74.2
CLOUDFLARESPECTRU...
General
Full URL
https://qqtotokiwi.site/assets/img/bsq/favicon.png
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.243.74.2 , Singapore, ASN209242 (CLOUDFLARESPECTRUM Cloudflare London, LLC, US),
Reverse DNS
Software
cloudflare /
Resource Hash
8c9e058f5ac226b78932825af939aa5aede8059bbeb5b73fc46a659cff4aa70f

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

cache-control
public, max-age=2592000
cf-cache-status
MISS
etag
"650bd9bb-6f5"
cf-ray
961cfe4239643e06-SIN
expires
Mon, 18 Aug 2025 20:33:19 GMT
accept-ranges
bytes
x-cache
MISS
content-length
1781
date
Sat, 19 Jul 2025 20:33:19 GMT
content-type
image/png
last-modified
Thu, 21 Sep 2023 05:50:51 GMT
x-cache-hits
0
server
cloudflare
vary
Accept-Encoding
GET
H2
200
d9d86b41fb079c6ff86865bc8f036b18.png
cdn.livechat-files.com/api/file/lc/main/15132858/0/ec/
27 KB
27 KB
218ms
78ms
Image
image/png
23.197.85.189
AKAMAI-ASN1 Akama...
General
Full URL
https://cdn.livechat-files.com/api/file/lc/main/15132858/0/ec/d9d86b41fb079c6ff86865bc8f036b18.png
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
23.197.85.189 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a23-197-85-189.deploy.static.akamaitechnologies.com
Software
/
Resource Hash
38fc568a3992ce46296d934589409fa7b6e51a3962e2391f020be73e45dbd170

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

access-control-allow-origin
*
content-length
27670
date
Sat, 19 Jul 2025 20:33:20 GMT
content-type
image/png
GET
H2
200
new_message.CTorF0S8.ogg Show response
cdn.livechatinc.com/widget/static/media/
11 KB
12 KB
11ms
4ms
XHR
audio/ogg
184.51.6.218
AKAMAI-ASN1 Akama...
General
Full URL
https://cdn.livechatinc.com/widget/static/media/new_message.CTorF0S8.ogg
Requested by
Host: cdn.livechatinc.com
URL: https://cdn.livechatinc.com/tracking.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
184.51.6.218 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a184-51-6-218.deploy.static.akamaitechnologies.com
Software
UploadServer /
Resource Hash
1d0bdbe8013ddd58bf31229ea12bd42dfe6bf4cb022cc65d519a45a13c403b5d

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Referer
https://qqtotokiwi.site/

Response headers

x-goog-metageneration
1
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=ZhCqLw==, md5=o3IRps/NpFNS1avP8eRGuw==
etag
"a37211a6cfcda45352d5abcff1e446bb"
x-goog-stored-content-encoding
identity
expires
Sun, 19 Jul 2026 20:33:25 GMT
x-goog-stored-content-length
11404
date
Sat, 19 Jul 2025 20:33:25 GMT
content-type
audio/ogg
last-modified
Wed, 16 Jul 2025 07:36:13 GMT
x-guploader-uploadid
ABgVH8-VhFXtQeMeFpcqqPkcXvAqJbWuaf-yiJBY3zv-Q1UVMdwFRwLfHywaxiktCuOn3BvZsIEY5IQ
cache-control
public, max-age=31536000
x-goog-storage-class
STANDARD
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1752651373539165
content-length
11404
server
UploadServer
GET
H2
200
20.CqQnL4Tq.chunk.js Show response
cdn.livechatinc.com/widget/static/js/ Frame EEBA
141 KB
45 KB
4ms
3ms
Script
application/javascript
184.51.6.218
AKAMAI-ASN1 Akama...
General
Full URL
https://cdn.livechatinc.com/widget/static/js/20.CqQnL4Tq.chunk.js
Requested by
Host: cdn.livechatinc.com
URL: https://cdn.livechatinc.com/widget/static/js/2.1K4W5B1m.chunk.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
184.51.6.218 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a184-51-6-218.deploy.static.akamaitechnologies.com
Software
UploadServer /
Resource Hash
8351eed3dc85a3f704518b3570d4753c8ffd9b428fb5ae67085ff1c5c1c59644

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Origin
https://secure.livechatinc.com
Referer
https://cdn.livechatinc.com/widget/static/js/2.1K4W5B1m.chunk.js

Response headers

x-goog-metageneration
1
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=N+DeHA==, md5=IQ9IdEeTwX8VgGsQuzT2HA==
content-encoding
br
x-goog-stored-content-encoding
identity
expires
Sun, 19 Jul 2026 20:33:26 GMT
x-goog-stored-content-length
144461
date
Sat, 19 Jul 2025 20:33:26 GMT
last-modified
Wed, 16 Jul 2025 07:36:13 GMT
content-type
application/javascript; charset=utf-8
x-guploader-uploadid
ABgVH8-pOjEm-RI6hcVQQy5YF48E6GhqKttf5Aod0yoHyqibQk-PiBGGpD6b-skOJ7wYBWcrrZBsq7Y2z-N1yg
cache-control
public, max-age=31536000
x-goog-storage-class
STANDARD
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1752651373513129
content-length
45780
server
UploadServer
GET
H2
200
24.CW-EwJ_u.chunk.js Show response
cdn.livechatinc.com/widget/static/js/ Frame EEBA
116 KB
37 KB
31ms
30ms
Script
application/javascript
184.51.6.218
AKAMAI-ASN1 Akama...
General
Full URL
https://cdn.livechatinc.com/widget/static/js/24.CW-EwJ_u.chunk.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
184.51.6.218 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a184-51-6-218.deploy.static.akamaitechnologies.com
Software
UploadServer /
Resource Hash
bbf58305f72fb15fc5eaff5587a0dd50f700550d43333feefbbddaa743638dd8

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Origin
https://secure.livechatinc.com
Referer
https://cdn.livechatinc.com/widget/static/js/20.CqQnL4Tq.chunk.js

Response headers

x-goog-metageneration
1
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=VO4JgQ==, md5=2D5wue/XESv8OabT0B4jVQ==
content-encoding
br
x-goog-stored-content-encoding
identity
expires
Sun, 19 Jul 2026 20:33:26 GMT
x-goog-stored-content-length
118665
date
Sat, 19 Jul 2025 20:33:26 GMT
last-modified
Wed, 16 Jul 2025 07:36:13 GMT
content-type
application/javascript; charset=utf-8
x-guploader-uploadid
ABgVH89MHfQjhoUcZH3H5ChdvcHRbk_5Th3cKkZrQhM-bx1hwIOstY-Fa-gi45o4TpPvlZshiVrFR-YAO4qryw
cache-control
public, max-age=31536000
x-goog-storage-class
STANDARD
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1752651373505851
content-length
37360
server
UploadServer
GET
H2
200
19.CD6tJ_A6.chunk.js Show response
cdn.livechatinc.com/widget/static/js/ Frame EEBA
4 KB
2 KB
32ms
31ms
Script
application/javascript
184.51.6.218
AKAMAI-ASN1 Akama...
General
Full URL
https://cdn.livechatinc.com/widget/static/js/19.CD6tJ_A6.chunk.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
184.51.6.218 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a184-51-6-218.deploy.static.akamaitechnologies.com
Software
UploadServer /
Resource Hash
635f81c0dd08bbcc66db7f78ca19657fc5661abb940773fc5716165aac9a5519

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Origin
https://secure.livechatinc.com
Referer
https://cdn.livechatinc.com/widget/static/js/20.CqQnL4Tq.chunk.js

Response headers

x-goog-metageneration
1
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=HTkCjQ==, md5=pom2Ytdcqj0YzPbFSAnxvQ==
content-encoding
br
x-goog-stored-content-encoding
identity
expires
Sun, 19 Jul 2026 20:33:26 GMT
x-goog-stored-content-length
4379
date
Sat, 19 Jul 2025 20:33:26 GMT
last-modified
Wed, 16 Jul 2025 07:36:13 GMT
content-type
application/javascript; charset=utf-8
x-guploader-uploadid
ABgVH891yTCfSJqc8XhMZfYfFHrEZytIOy9fpO6wAclz959VAUFY9eFDG3KPmgxEO8r8UB_Oa8ZcxgydVrKCZw
cache-control
public, max-age=31536000
x-goog-storage-class
STANDARD
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1752651373463905
content-length
1905
server
UploadServer
GET
H2
200
18.wuJHqzJS.chunk.js Show response
cdn.livechatinc.com/widget/static/js/ Frame EEBA
6 KB
3 KB
32ms
31ms
Script
application/javascript
184.51.6.218
AKAMAI-ASN1 Akama...
General
Full URL
https://cdn.livechatinc.com/widget/static/js/18.wuJHqzJS.chunk.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
184.51.6.218 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a184-51-6-218.deploy.static.akamaitechnologies.com
Software
UploadServer /
Resource Hash
0b1641f07957837b52e0cd25f0503fbe778b1f8a5d12324d3942e110cfeaf23c

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Origin
https://secure.livechatinc.com
Referer
https://cdn.livechatinc.com/widget/static/js/20.CqQnL4Tq.chunk.js

Response headers

x-goog-metageneration
1
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=hYpdmg==, md5=xlcYgs/edu+BW+SoCC1GIg==
content-encoding
br
x-goog-stored-content-encoding
identity
expires
Sun, 19 Jul 2026 20:33:26 GMT
x-goog-stored-content-length
6145
date
Sat, 19 Jul 2025 20:33:26 GMT
last-modified
Wed, 16 Jul 2025 07:36:13 GMT
content-type
application/javascript; charset=utf-8
x-guploader-uploadid
ABgVH88osgJJ-Lj1TiWzb0P6YCpjM6cSilEJqxEhI7NeePsyUqYcG9kV8dE_BLVF42Gf556p7h6Fypn-GVhJOw
cache-control
public, max-age=31536000
x-goog-storage-class
STANDARD
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1752651373450501
content-length
2526
server
UploadServer
GET
H2
200
16.DiMdnp9b.chunk.js Show response
cdn.livechatinc.com/widget/static/js/ Frame EEBA
1 KB
1 KB
5ms
4ms
Script
application/javascript
184.51.6.218
AKAMAI-ASN1 Akama...
General
Full URL
https://cdn.livechatinc.com/widget/static/js/16.DiMdnp9b.chunk.js
Requested by
Host: qqtotokiwi.site
URL: https://qqtotokiwi.site/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
184.51.6.218 Singapore, Singapore, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a184-51-6-218.deploy.static.akamaitechnologies.com
Software
UploadServer /
Resource Hash
277b120faabed5c56d60b28533cce62bb536d93a8e5373945e0931b374b1cd53

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Origin
https://secure.livechatinc.com
Referer
https://cdn.livechatinc.com/widget/static/js/24.CW-EwJ_u.chunk.js

Response headers

x-goog-metageneration
1
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=9wz97Q==, md5=UYwmE/OqbZwZASKhl7Tvrg==
content-encoding
br
x-goog-stored-content-encoding
identity
expires
Sun, 19 Jul 2026 20:33:26 GMT
x-goog-stored-content-length
1163
date
Sat, 19 Jul 2025 20:33:26 GMT
last-modified
Wed, 16 Jul 2025 07:36:13 GMT
content-type
application/javascript; charset=utf-8
x-guploader-uploadid
ABgVH8_wSnmyzXZ-oq8oKEi8oayeOlWP2AnmmWkBtfh8csuMxNYAAN0viBAfaf55VINZR1AomWXK-A
cache-control
public, max-age=31536000
x-goog-storage-class
STANDARD
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1752651373457667
content-length
557
server
UploadServer

Failed requests

These URLs were requested, but there was no response received. You will also see them in the list above.

Domain
masuk.sgp1.cdn.digitaloceanspaces.com
URL
https://masuk.sgp1.cdn.digitaloceanspaces.com/images/games/gatot-of-kaca.png
Domain
masuk.sgp1.cdn.digitaloceanspaces.com
URL
https://masuk.sgp1.cdn.digitaloceanspaces.com/images/games/pyramid-bonanza.png
Domain
masuk.sgp1.cdn.digitaloceanspaces.com
URL
https://masuk.sgp1.cdn.digitaloceanspaces.com/images/games/aztec-gems.png

Verdicts & Comments Add Verdict or Comment

67 JavaScript Window variables

These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.

object| 0 object| 1 object| 2 object| 3 object| 4 function| OpenInNewTab function| $ function| jQuery object| __lc object| LiveChatWidget number| chrsz function| hex_md5 function| b64_md5 function| str_md5 function| hex_hmac_md5 function| b64_hmac_md5 function| str_hmac_md5 function| core_md5 function| md5_cmn function| md5_ff function| md5_gg function| md5_hh function| md5_ii function| core_hmac_md5 function| safe_add function| bit_rol function| str2binl function| binl2str function| binl2hex function| binl2b64 function| str_to_ent function| trim function| md5hash function| md5nohash function| proteksi function| gtag object| dataLayer object| dt string| current object| START_DATE number| INTERVAL number| INCREMENT number| START_VALUE number| count boolean| __lc_inited object| LC_API object| google_tag_manager object| google_tag_data function| _0x178a function| loadlink function| _0x335c string| randomtextnumber object| html5 object| Modernizr function| yepnope object| respond function| onYouTubeIframeAPIReady object| gaGlobal object| skrollr function| parallaxInit function| target_popup object| regeneratorRuntime function| getData object| __cfBeacon object| __twttrll object| twttr object| __twttr
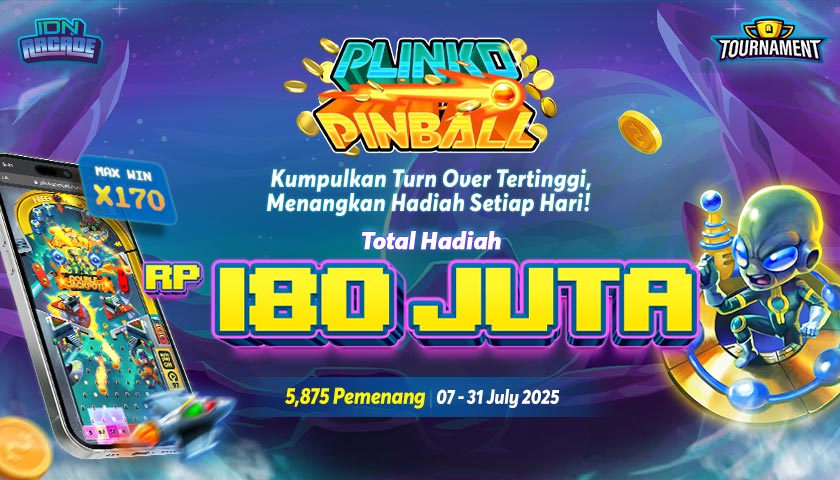
15 Cookies

Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.

Domain/Path Expires Name / Value
.accounts.livechatinc.com/v2/customer/token 1970-01-21
16:31:57
Name: __lc_cid
Value: d9556e98-2031-4d5d-a929-27b14dee8571
.accounts.livechatinc.com/v2/customer/token 1970-01-21
16:31:57
Name: __lc_cst
Value: 0e19a966f51cb72511e103d2bbf6ffe97b911b6839b63638f6cc3f085833d6c2e2824cea1a11e54e5cffbee95dd11a816c732117e9f9c83098244aa89c04
.accounts.livechatinc.com/customer/token 1970-01-21
16:31:57
Name: __lc_cid
Value: d9556e98-2031-4d5d-a929-27b14dee8571
.accounts.livechatinc.com/customer/token 1970-01-21
16:31:57
Name: __lc_cst
Value: 0e19a966f51cb72511e103d2bbf6ffe97b911b6839b63638f6cc3f085833d6c2e2824cea1a11e54e5cffbee95dd11a816c732117e9f9c83098244aa89c04
qqtotokiwi.site/ 1969-12-31
23:59:59
Name: SRVNAME
Value: 99c
.qqtotokiwi.site/ 1970-01-21
06:55:58
Name: __cf_bm
Value: wca.Rp.MnYHc6I6cKi0SQNbjnkC2T5LRW4Jak4Wb0Z0-1752957196-1.0.1.1-R0iZKvAwRn6Sc1JRq0rpJFPVbz4hJauBDRXCFnxQSCRzcDdNLZnRaduGNfZlwCasl1Xoq67MyUz4PwGk9fl8bbjEirOQln9u6BzNNruH39k
.qqtotokiwi.site/ 1969-12-31
23:59:59
Name: _cfuvid
Value: 2GHhBBgGpoPhUVWPKXzlZasEPf3QfTAJ08SZYV.rIr0-1752957196313-0.0.1.1-604800000
.cdn.areabermain.club/ 1970-01-21
06:55:58
Name: __cf_bm
Value: yiPX_5ZxbS0nkqfKYa050l7xkG5O56syZPbVZRrbYuY-1752957196-1.0.1.1-gVFu6IRDCnl3cZDNo7S6Ik6GiXGzXKx7q5y.kExWFGgWscOu7enCBzr1cI1JK5cz1vvAgnQIj9FDGsWhE7CX2D.FThqIBhgDtKAftL6IYb4
.qqtotokiwi.site/ 1970-01-21
16:31:57
Name: _ga_SSN8YGQCHV
Value: GS2.1.s1752957197$o1$g0$t1752957197$j60$l0$h0
.qqtotokiwi.site/ 1970-01-21
16:31:57
Name: _ga
Value: GA1.1.374633845.1752957197
.qqtotokiwi.site/ 1970-01-21
15:41:33
Name: cf_clearance
Value: 8IbNZ.kkwRb_KXimD9Eh2v6jMM6B3DE96rTOeSwBxtY-1752957197-1.2.1.1-qCg465Qj_RKy4lWL_LJ4p2wgpZdy9HIH9OgM8ID5I5.jp4dCUN5_0QEgh70l6pBuPZJXTIR7d3OCa.BFRuxQx3QYYnAyp492S4jkkpgtyMDEDdOO_lc3nQRCpO1X9oJ7YO0wWOeOIKdZpP_c4d8z3Fn2oqLkqGB2hUhTu3OsV_GSDCZc50qJjwuygfNdY1DnFMFSAUefYeBmJVjCMAl66SZRamDpLavK5lqmTCq._Fs
.twitter.com/ 1970-01-21
06:55:58
Name: __cf_bm
Value: OfhMOL1U1lSorRRkEprQMMwpsHrscabAeA5v0soqJto-1752957198-1.0.1.1-LnhtW908Oq7XSmaQcdscNDl63nNSHEdk.x._sDzfJrAwV2R_czXl8tnk.gWklIfdTrzPyEaskpwYKbHJP8r9JqmSzNq3GQkiDiOIgxna68Q
i.gyazo.com/ 1970-01-21
16:31:57
Name: Gyazo_cfwoker
Value: i
qqtotokiwi.site/ 1969-12-31
23:59:59
Name: laravel_session
Value: eyJpdiI6Ilc4NXQ3L2thR1NqV3lhYmZYUTUwc3c9PSIsInZhbHVlIjoiTmczeFVyWnRnSWs3bU5QeTRmVi9ZTmpIWC80azQzOXFSdDVRNWZYUSt1UEt2eFBKZ2c2RWhsWGUwRk5sUVBEN3lKNllhUUhMWkh3QnFFblBzV1ZZM2ZGRCt5TzQ1VnRsL0RUb2xGU0hvZytRQnMzZll5U1ZUSVBKZnVlU2xqdllpL0FWV2Q0L2J0YkdhbTZVTEJFellHeEM1TkUvaWY3WkVoRmo3YndIK1M3YUlLNHFBbFpqeTdCNlNtR0wvMENnVEo0aTZZaUhERTZROTVlcU5WcGVhL0FsRnd0cWZFYXJPU0ZuWDJzMnBiUXJCQUNiWjV0ak5paEZSVXo5THFTSHpQNUxEYnJWMHRpejZGamVFSTFPNnRUWWNFd1FJaE9vTjhjR3UvT212d2U3aFpoWVUzSXFlaVVDUmg4L085RWlwdzdtZnBHWFBRQjJBUmQwVTRtM0owRzdVZWNTcGdyL0twaTVYUjZmWFI2OWF6Yzh0bSs3aWMzT1VNQ21Id1pYbm0rbzdkRzBwT3I4RDgwb0xEM0hLZzFiQUpTSHh5cHFMd2x1ZEg2YWlEVFNheTNvdlFNTjB4RWkrVDZZbnBIZERkbExkTDh4dU1PSXA3WWUxUExLRnpwVzNLUFZncnhUUHY4bGoyMUgyejNEaVJkNWVTSFVZSER3eUJCVGxESWEiLCJtYWMiOiI2NDMxNGM4Y2NiNWZkYjAwODQyNWQwYzU2ZGI3YWMzYTBlNTA2ODIyOWEzYjYwNzk2YzY2NDc5NWU0OTA2NmE0IiwidGFnIjoiIn0%3D
accounts.livechatinc.com/ 1970-01-21
06:55:57
Name: __oauth_redirect_detector
Value: counter=1&t=1752957229&tag=57c25db2f63c57e69e2c678764242e67c55690fe

3 Console Messages

A page may trigger messages to the console to be logged. These are often error messages about being unable to load a resource or execute a piece of JavaScript. Sometimes they also provide insight into the technology behind a website.

Source Level URL
Text
network error URL: https://masuk.sgp1.cdn.digitaloceanspaces.com/images/games/pyramid-bonanza.png
Message:
Failed to load resource: net::ERR_NAME_NOT_RESOLVED
network error URL: https://masuk.sgp1.cdn.digitaloceanspaces.com/images/games/gatot-of-kaca.png
Message:
Failed to load resource: net::ERR_NAME_NOT_RESOLVED
network error URL: https://masuk.sgp1.cdn.digitaloceanspaces.com/images/games/aztec-gems.png
Message:
Failed to load resource: net::ERR_NAME_NOT_RESOLVED

Indicators

This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.

accounts.livechatinc.com
api.livechatinc.com
blogger.googleusercontent.com
cdn-icons-png.flaticon.com
cdn.areabermain.club
cdn.livechat-files.com
cdn.livechatinc.com
fonts.gstatic.com
i.gyazo.com
imgku.io
landingsplash.xyz
masuk.sgp1.cdn.digitaloceanspaces.com
object-d001-cloud.cloudstoragesharingservice.com
platform.twitter.com
qqtotokiwi.site
secure.livechatinc.com
shareservice.net
static.cloudflareinsights.com
syndication.twitter.com
www.freeiconspng.com
www.google-analytics.com
www.googletagmanager.com
masuk.sgp1.cdn.digitaloceanspaces.com
104.16.79.73
104.18.16.236
104.18.24.163
104.21.19.4
104.21.48.1
125.56.219.3
142.251.10.113
142.251.10.94
162.159.140.229
172.217.194.132
172.64.145.29
172.67.162.223
184.51.6.218
199.232.44.157
23.197.85.189
23.32.29.106
23.58.144.63
64.233.170.97
78.46.22.9
92.243.74.2
96.17.96.8
01ec6b9344c49b01b68053ba12874ee4440b31e569a8838ee5eb702846ab1986
034ae3152431795278b88fd9ecc51ccdd6ff6f3be0f482cb741c82ee39b99cc9
03ad483edfa06ca008b7c915c2d1f9859a2a8c02ac072764e90fbf56723b2ad8
03faeb81ae851f321e7b231c7cdf0d5974508e0f3678736e8d896399df9de811
04f53e275240ef1c293ba4a40873657150254683cca3b8129ea63b98dbaf541e
05293928ea5187dc9cb2b18f7e32ebb6bf4450888aa413b98551217108c0ea61
06a8853c839d6f33460be962c875acda97272820a211581017d806981b3d343e
06de4fe93f009e650e7afeb27516d603019d8721cc0e236eff8a06ef4abf0520
08a9718be96d0c889d30ba490bd7c570a61d0fc90ebd170a42c9d856d2f29ac1
09b2dd7108d5be7504d9cceeb879e15d7038d60290ba856169d399efb469c1b3
09fdb0950475d742154da396ed6d6591b899bc7791798554c47cd5ad8fae1087
0a0ebaa25971f58c3366e5c50f4a3b843a758239c718fbb16190f117364d1bdd
0b1641f07957837b52e0cd25f0503fbe778b1f8a5d12324d3942e110cfeaf23c
0e084ab771422057dd4d351537103d7706acf5019b9dff17e09c870a9da6acab
0f06109a3edc4b5015427cb22d029aa91a72acd32b71ce5079818fd6598241a6
1100977a241133f42972e197c28a12254b88b7b512eb3f4a8d79f3d7ef8a0084
12e07c5213b4a6672dccc5476c84e78c7dc2819f735f52941fc8afebcd343a63
1434ba0052bc740077b0f0e245abce35b1c901e9b0db19521956a70e8b3409f0
157c3fc50a9a79068835c64a4a57ad51f33cebff9c177e171e632d1e99134b84
16bc998d0c596a493cc28faf84708de5b6b0e15e854599c1f19d350299d3fc23
173460e89e6a7244218badae2016f65c48a3eae9d400802273eeca18b07336f1
18fecb314e57ea301647fb7dc124e46ce11e8bda6a9cf73d4f368a6ce8d9d746
19afcb54d051bc5f6897ca91dc7c92b0ff1993f03379f0a7b2182edbb672ba68
1a7ec5702c34c0416ff05b6186c80eda3e7752ce1fd0fa271b62839f411b868c
1c34b1ce3038b7de035f61ca1ea0908230c2e3a8f6b01b261802034f3e8605da
1cb5bcfaff8d285c2f72b11cd0565f3aac6859db3faee815dc2c37cbc06146c9
1cf7f50f40a8868a0f1821986cf3a2c029251cc88b25bf9902fcc7205234c8e6
1d0bdbe8013ddd58bf31229ea12bd42dfe6bf4cb022cc65d519a45a13c403b5d
1d3aae39974bf5c4c9a42385e1ab95ea7c3c32907013dd8ebe74dbcce997377c
21283e24743d7dcd1055c1caa8ef55a0d1200564029851e3b61af78cc44e68f5
229c5efa60567b67d2b8513a5c5944c75270b0f6f32f394ba9a540a5a5de4870
230d2621d167db30fd785686ab9cfc012bbcffd63a6c46a35a56d6ecbd21c330
2317595b2f5391bfa05f57b2557c1d361131dc6392f1957f396b99b4865731da
23babf3b8105e414102c6bec9c2e4f6a2530d23ceae3712c305e7ee0ea6c91ad
23d2b335b6210ff91d9d438cad7f2301456f0e006384ef95f353f120dc374586
242b7574df69b7f8d4d0070a4b741ef1b9155ce028c505f0b97fea2de6247728
26e1a00f0ef43c5c524e9523a26351d1f07736166d7921ec622b458a41f5b73c
277b120faabed5c56d60b28533cce62bb536d93a8e5373945e0931b374b1cd53
2a41dbcf98569ab4112d305bdaafeea3707b37c11ab842011dd86186ed1c65be
2adefcbc041e7d18fcf2d417879dc5a09997aa64d675b7a3c4b6ce33da13f3fe
2b735a9ab21e15a9f70552ac4d1f479b4df7bf5161a07c1bbee610e00798c3f4
2ba33301ad4c18efc75b8f59b9bb315ac909e06a851004460735cb6aa7213a72
2c4f35c70137a8754b6a2ff493e9acf449c05c8197fa76d80cc66a897aef4d88
2cf27574ccbf4334c03240da6954708a93ff08d704c4ef850748c8c6df5936ff
2d2a7ab1708e5aeee4123d037d8484e9e4c3cca489b4b6b3b931143911403134
2de6a4f3964c03bb35fb9d54b3de00ac38330f5cd91389a3d462269c27775373
2f75efe3c598d795e95fade1746451bb15e1e950724f34155195d4d6e93180ae
31355131b072132880901e635c3d85f8db3b9994349b181fb747f8bfb24b706b
34a8ce7851064d39b82eb6b4a3ae4ae9c868ffec2c5b013fce13db1236bc22a0
373c4996ffff18406b9e4ee2ea524168ea17965804e7500925f975b4c21f1de4
38052b1a4b563ee810478ffba5f8e43545d8c3c2c91c1b35a5a652498eb406d9
38fc568a3992ce46296d934589409fa7b6e51a3962e2391f020be73e45dbd170
3959c050f2dc63d06764e3394c3190068e60e6c168ebe9a532e6d61c9dfe0530
39fc7afde669d336af3d05eb3f9d58c42deef014e7f1a62e2d231b2b06ab88bc
3a64937a464b2179a78e9d35bb372d2394293a9bd32f398f4e655ddfcd70a53b
3af52c81706f514c13476a4bbe38e792d3dada08fd7ab0acb946277c175f959f
3b7aab0ffdf2bff2d0eb0c6441b5c59a4a125a999c08471517e23ca9a05fcb24
3be5d62f547bb6c65785303b2fb1bdf8dd1d0fdb6f25d10213fcff54bcd7a357
3c1fac4135f8cc39b41d72462949f6a3852301c5aa228b0e372f3eaeba477b17
3c4de5acb67c63e93aefa4ae398c9b96b204515b0932d0be82f00edbb400b9aa
3dc7ebef252de063ad78d19f0bf1bdbd8ebf4396c96caa919e23b9465081c70e
3fc91417ca2b2f55d5f1947f8eea9d27398e9f0d1b13f078a5d16a8a2d9368f1
41394d817f909ea1d7d35a3652e3d1a661731ba3380312d55f637cb9b5de7c70
41ccc06f3885a89caebc9f7a6b3140a24f33dbf774eeaf79ab7d74fbdec6c82c
42267f804c24ca4f8564f7f143a04ce6f23840ca87a89eb70df84e8aa2862e7c
431cff4d223f3296f7d4b543573271745a91d9069a3666844fb3b037aad844c7
432c6730124baa271718e80f940c4c680522619658de6a581931348d43e06b6e
448148caad199e5db2c080922b6e144247efa3afdb52c0ab682cf9a5c729d352
44afa7bac070be11a25113dd4ced630691439d7801bb9fbaf0b2251776d1e558
45acbaae00fb0cfa8413b582cd4c0dad9653c78a051a7215205079ccc7c7e233
45b1d3657aa9ffe34c9fc111ed09d06936e9379e5698c19d4949acf581415274
45cc85f50998d7695e5f219ba3348a7ef4ba407bcb36bbd7fd8191acf9ade8a7
47cdc158a57807d545f39a108f30af35dfbb13d7f133abec3703f0ace15f660f
480716d8867cf2a50d97fabcc04759e81de1259283ba3e2c4c0c1d46995dc6cd
494e58831398fac29d99b39418c070bd8a06f997c84b222a59003da9f0771168
49a26f1b764c3e81b6b831b1fdb642868e6afbdfe79341fd29ee3b08347847a0
4b18105a346260a3e8359cd02633fd5f8bb244f2d5f43e4375a1efd10e5c865a
4e02417535468c9d74f33333ea8aa01ee1921f11cf19de61d1f9b1288ca9019c
50afebd206f7b1ef8fcf1d4dff496412a08518bc068319f97465908441cd4041
5143d80cb7714a2fa2526dbba0870b76bb3255e035f5d7c4bc197599562e0cf0
5164805006e9213e6b33a236232a9b89b00b6138944d0486776fae98d16a059e
53198ad95b9eb6ef70ec8f46c1da1ef3d17e7c22557c8fbecbf0aeb6090c80c8
53575d3c511655350ca6fc343a0dffa381b86cc844e5a489fc019f74ee9087c5
544b151ad8c7487ebcaa8538d1c3c18b2a100720d6fe9ef6ab74fa93d5c638b6
57e835e319be7437c1b26c2830fc2d401826e983c3a113f2dd1fca3fe65c6b7d
598733cd63255150bf43721d0db1234d9512be150fadda472f8ad7876117791b
5a7fb7e9f2768a5219181844ef6b6d35d546326f1e47af6ce2dac86634be5ea5
5b16d38dc650b9dc34e7564e823ab67bdbc69f81d0a79e0d61c0baf788744aaa
5b3ae7f7234863a0775b214bdeaa9f44aa4a3e06163e03486f45ab8067e90b0f
5cac9c4ea7470f69937f3e0c66643af243f022ba1d0d1b92ea0b891be8d3e708
5d19547b40e94ab90e831bec03fc23d4b894894bb93006b3b3fd8d62e2f355ca
5e829a18cd9f27940b0bcfd8cbdc4395f368de18d89fd96bf09fcd5cf267a58a
61e4384b213f36a3a7fc08b44510fd439ecf3c8523b8633f723fb1012d2fbfbf
624bb12055fe7dc2c6bcbe9a58b27858700e0c91aac333844b96997792aeaf65
62ceb8a88b98bbe24a3b9fd8d65f58988e3b424bdb754e8d3effcc2d18e6d6c2
635f81c0dd08bbcc66db7f78ca19657fc5661abb940773fc5716165aac9a5519
639775068932c1b628a731e51f57a420b6006929bf08058d1dd628b2b0aa1e51
65723a3f6bf46e95bd82bbbc3f986c0df44ad1b4427abbc3fa252a53ff40b4ea
66c48e4e8b96b3ff0550da8ffa663d51b52337dfc7df544544499f769cef5dcf
678b72a40035fb2e414d41e9c938856b7d831eb6f364a35369f56c239ab837ba
68e6fc98225baa9cb03f1bd4875cdf6af3dde125fd0288838891474b3551416b
6ab9b998562575fb94fd0ca515cc9e41510748c81bd9817ec256d92198370919
6b41e47a54aefc08aaa3678ed56f5689ddf69b8e8a48e9af8acc200ed0559fec
6e148df31d721a0ff08563f2d676751786e01418c86ee54ee8f0e88aa46ae26a
6e173c68d135f300595874b5116db86cdebf11d35d5a1b26dd1eb517190e6896
6eaa0b875e0b645445f4e6d54c92397c90f2124cd8f2e5c66c34b18a4b1e1d0f
6f78df7d3286f40fde31a16161673e4ea46ccc4fd7845eb84f5e9eb4219f235d
70c00445d6632039ed99af760731daf3bf60eb12061863ee61e2cd7276a54d18
71dfe3342d07e446916111fed9de1724bdde56c963c1b2573b7ec643e9f26e50
72aa7aadeb336111077533c97969569bad512ab8b4af33c1c220456d3bbf9580
75beb6ea66cfacbbad808671aa6b753ef5c5bf4e8d5efb9adf9cb840379ed803
796951855984fed308feec350d31ea2ac1382b2c6aec06412f9c33e1c13fe075
799aeb25cc0373fdee0e1b1db7ad6c2f6a0e058dfadaa3379689f583213190bd
7a1f1a71a4f70ce28960a0f908e973b0581e7ec579bd2dd317ba8e57c4ffaad0
7a61b3be6a7e0f1d32640743dfc716b6cf753a7f5e8df400c5f9b89a6982daeb
7b1443542324668d2e448a0e87bf84adedb4cfcdcb848848a66aeb931990ba25
7b709c330e9b8e972a00555a1e6f03c77ebbbfd167312c36efe22b208b047d90
7cf0b8467b88360e4e11881a231c013464a4fe2c449887baa7fde731a7058845
7dce1c4a3bf340cc03d5e65996820a2c972c7dba7975b3084a71a25ff144046a
7e765c2504b17be43c58806872d6c4a0fc5737f6911613ec17a4945fc7aab66a
7ea9463fbd40b0522d7f911faba3d5d87ad8de6c4d75e08cfbf907c6e098c27b
7ebacae5f7c966d5958232cfb7b6caec90e5f5163b80914ef8661c3cd342ad5b
7f1d23659e76eca87d310351b7598a64201f99a8be2a947319f0182cdc3b0cd2
80353503e48ebf6c2ae9f70184d3e758f64bacf48afe147e039df807509200cb
81f2e2a5c8a7ddaecc142e943f0cc8ecff171c000576f7ce2975c3440565d24f
8351eed3dc85a3f704518b3570d4753c8ffd9b428fb5ae67085ff1c5c1c59644
8471a9d93167c8749a7d3592aa1d3603d4398a519712e176918004b21783f888
84ea548fcb5708e5d568d81bd06be83885877333c05b8d8f3378d0035f7a17e5
85513a5018b7431d4bc6e4743004682883c61c18fef2f889b332b61fd6f4ff8e
87d23728128b2b6f2af147c7c3c7e155d8a983a6ac7484303539a8c08028d847
8a18d13015336bc184819a5a768447462202ef3105ec511bf42ed8304a7ed94f
8ae9a41def07afb4166b08e3143071437d1867e5f26e6bd907899a8b50bbafbb
8b2f204a6ecba604871a339562709f1194ae9ab0a2c8ad61564e4788682b9f2d
8b476f0ed400347d7a4039100a4f8baae69eb909109550177d5a724a3aa8e793
8bbe4c8b419311ed94a24330552c10ed14983465b5c82613ab5d2d74fcca4e9a
8c9e058f5ac226b78932825af939aa5aede8059bbeb5b73fc46a659cff4aa70f
8d1d81653665b6167ced0670807c2fce6370e8aa0d48767f6a68f6cf1148d8b7
8d8cc7cb23823ac85dc7eeba0e18de86d687fb6d2834c7cdbaef1aaec2171086
8ec44a4b321f5115d8760f193298585d8b28a26dd3190d0a3690b9e09a489a94
904f55d535ef456b9d3b9e409ec7a44e302198d3352260914e1691d072ccfc4b
90b8ed7f6774107032908ca66b18cd62374f85d4c0b607bbabc8e2bc00464483
911dccc7a59863b46d628fdac57d96a7cbf72325fe2555d2a3d165c6258d3464
925c5f504b1c681a841eef511ec610622626d728a8c5ac51dbe79d9251de1c88
944e25293de1902e94503301ab274b4348c7d48828414eee613fdbfc614dd74c
94a03d94ea079e4a5877a8d14914288246f30a12b3833c8d59ad22dffc63a7d1
94e8ab01225044ea5cee0572773045dc3193583f730ba68df0b551bef0d88515
9531877a395471eb20e85f9e742bf48cde70d1e528d9aaa55c1c210fb3dbf811
95df7f4d192968c5c68e43a936016ad025fac7ce02a221a1bf13be6592667c30
97e599f952ceae0ee2e64cf0f3484b8d08c7db8e7f959effa33b19b8584b48cf
9881bc01e3ea57d351587a346c64a63729f1bd7e9d63e4e1345e9ccc2158c85a
98d0fd56a39f3d137dc1b2d799b66d7270d7aa843d3a6159d2846d16002c0cb1
991994866beb5e90d2205f4c5d4a757ddd38c6399386335991b260a89d857fa1
999ec2b7964f85511e64002f8210c9b3447307de01d212938ac0d5d8db7ef952
9b5174294cba545cd6c711f8b6a614d2782f70b82668bfd0229fc91c250adf97
9b9a493c7bd4e52c7d5980ea409e80f34d8d57b1cd999e67cad4d1650dc8275a
9cfc116f10c364fbd87b3f19a857da113ede59aedf1de28af2b87ec6902e6c17
9ed14a2ab28233a8e331466171a487ca4d5645e8a58f5a7748c3ae19dc9eff2e
9fd10c2231584196fe8da4c4246b0c00296a137cc2f472fb247eb5c0044aa444
a379b1707064386da00957301b6eb053249cfb462047d44e4fb6d52898f5b78b
a4849987d73f343c8692c5976efb0e4f4ca25d9182ad0206c6cb2b9e7bc1539d
a5ea9024d51dc1611dfb718849b48c24e6a09114c0da31995f58551326074b57
a6f8e423ac60837d470b983a555446cba672ae4ed02b90880e7869d79088335d
a76090f2d604a7e9bd429900001b367ae94f52d749fd0f94706be887d87cce7f
a796080d67e5e42690ea948ab2e7d5b574f1a385e1dac5340b1d56a44f49c73c
a9aae7f8a5dd0abfc486c0f4027795598ab0330d297e515376333d24e78385f8
ab0a5172b61d1425fe64a91df72ae29f2baf35a7b5b678dfb994781b715309a7
acc0849cb6eb4d29e53f9002dbecee197245e94232cf6dd2eb7342c452d6e40f
af2012b0cdfa449f186df2f8dc9b3e64b48b8c5c630cc8d3c4df61973499e7c4
afbf313c9cd8546932da922fcd36f00f9e0787370ac0d46ca82d3cb31d15d0ea
b12ece59f277365ed73739c5f55c9d9ff097d137185ddeb95885249ff97c6ffa
b47d1aa45797ad3e5d33d3ad0dbc0485308e8e4fd034794288d77f64d1050a04
b5ad811f2f5be0756f9ca9df4bc094c4734131774801af0c0e00322bbef218b6
b60a19eb59f86325af0f4c3e4736e6ed7f3ecc1cadd6efe316e90ae7a75f0ce7
b725c5ba24cf4a20d1705ff7f7e75e7af666845d17c514b2041da4e4198cab77
b9506d56c2cd3db1ccf10c95c053d7efc6cf5199baee34cdcba665d1ed7542f4
b9c4dbdfba5601f8435783db29e4d6825ab5a0077c75077da62fa2959e787d38
ba75543913b3258b7a19cdea608c7cc47322898d244b40b6190c970be2d3a2fd
bad488c696275e38b9e95ee1c7c8662b01705456ed3049d191fa66b0bd575cd2
bb33c75ebfea05c8a890cf324caa643447aff6ccc845cf1b6877d9d0ed214a61
bbf01f68b51763c5e87b9dd472a6e585a32aceb4c51a034d7e8353d6b32d4f38
bbf58305f72fb15fc5eaff5587a0dd50f700550d43333feefbbddaa743638dd8
bc125921b5e4dde1c19d4fbc0a6ef3ea616eee9577822c96b29789b7f69ba5fd
bcc36e6dfb15f4c5b87dff41e7f4007cc49b1bd0c460ac5d5e818b4e3a97b2cb
bdb49593241ac3b4ffa1a72798effc086924f32ee7ae14c27002c9ff32600090
be2842f543dc56cb96df830123192738fd492fe990fd69dbec12270fabc5bbfe
bf2d2ce2803063fd72be8165d5fbbc700e24dfd6bfcb351f064367a90db9ef4e
bf58fefb87f7b329edb0489d7ab7820932d2037655c9dbab7ee89b68cd077ace
c0ace412ca1cc23ec09d653937cdcd8672bda7aefdeddc330262b3c7bb833f22
c0b8bb9e086cdb5d02cf833f32ac76cbd382f0bb9d0a522d704c0819c5bbbd45
c1a088ce29b0ff0b0156c7ddb22232029c9d12382dfb2c62b04bba67db59479e
c1af05964be2562a6bbf7c1d8f2a19554198d2e2c1980454a2b8f61f307772ff
c1e6c3f3fa6029282b8d718f2088fd4dfd5ea272fcb63bc37f95e66df9918df2
c2384f36a74df3707f44499728e72a777bd3fd2b430caf7d4b0701e711d0b8f2
c24b18ffc29b98248f2c02397ce2ef0c777d7d4f2ca18800154e39d021a6010f
c3bd5f5a73de3e19fbfdd13cca576b1d17b6d84e3a9a7cece9efd4726899f1f1
c3d46f64e06d98e5d467a140ac28d8fe3f17eeb0b05f6afbf3a4742bfbe48581
cbdd8b7572a4b646b8e016a55904309399dddf483be439380e8997106bac0786
cc9af994a65e2deac1f388408504e6a4059652a5c652bcbfd0898731b9153be0
cdb2cf36dee34d0495c09e2601bcd528ba63e01da77c3fa4adef8ae34944cd70
ce416742adf00033170694298361d4824de9c49c9c0f66137190811ee11e53f6
ceba2f1142d6a9fde6e9ce01cc9367428710b37d2e9faea839cc5c3d34966dfb
cf6071b1e482ced4345fe12749d8cd348290e03bcdc1baeb8792f81979355b00
cf91122176ba6cadc04f42930dd19b4f8db1b670efcb5b9d8cdc18696e3d1a65
d23aab8e833179400063e1973b4ed9d50cb39ba302bb99ebb1c1779a1e2c1715
d2eef1bcb32f4a121cb14ee6890dd34cc8aa9738e456cf8358d06d137c508402
d3b76fb03a7607b5da00fc0252be26fef8c76a0b68feb2ff19b439eeeab3f705
d4254882a1d386be367b1fce78e596f295a4d3739e31e1fb57537b862f9d1710
d598c8d0887f398f5e3464aa37a2bd77cdff2f9d0d846b2d91a86fe85610cf8b
d5a2dc8181d675093d1fb20ac43e86ef38bdfd8f1b3326db0da54d12d98158fc
d6169df2dfb496b6e72e017e8f3c8c6e241f5db25128474e64082546e3155035
d794236461f2a50e252c3a5ab3230fc1fa42d7b5bc4084077931e7d4a03067b6
d7a54fdb553b91383f1d6f043d10573d88dd023370e76f27e86544dfacf9ce46
d942e4f9b28cd8cfe2961f8a40919d77a8548e8341782c9c129bccfb87dee632
d943adf3ed1dad80fb33a3380e56e5a584293f8d1694dbb6d5c5d1c6036ee406
dc6ad4aa6efe488b3c2cc362183d8a2420dc87e484587cacc46dceac4a6b84f4
ddd7216743eaedad035bc59bb6f92a22b5758e370f5ad7417bf55df663a20803
df04e5456a26d89d36120c6078dadfb6e84b37b635c5b8f75a1ac75c27e1fc41
df344411eb3c7585c6398e1b38475fcc3040ccdc4007ed707734d46e3a50843e
df5bfec8fd98e9195fb9f02960c1f2a06deb9f024dd04801a45b772feffbf5dd
e00749ed99da6de8ee85c1fa969a7571feaba5a506c1dd88be8a12e20ed680d9
e0961859c47efed5f047049178bd6c106b198f5104dd6bdf81b301682bc98a3e
e2939ae51cd455bd9cadbd0813f183ac6ce21f453bae5903ebeb43f8e18203e8
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
e58260e204b97def3d0cb7c8f11c0ddb7e2255eb43f20c05cd9578dd3b6a31d9
e5fbca3a78b54f9bf7ef5a205a5d6264b74e8026943ce6523b214d4bacf78761
e73672b9ee5ccfb007c410d8b9d4455e2514a7d7cb2dcf971572dc289bbb9c5b
e7f471995cff2d274f80d9c96d3d4a066d8731fcea2d52446a93d88bd5e0d878
e8a7b2ed05fcc0a064737d127e166f8e81781b746b70d8e9aeff7ad0b055464c
e9a92140a373ff5cc04f5e6238a71b7507480ac81df6a192636e762635f8d4d7
eb031bb8465ecf1226855bddd88351d72ba66157d0330964d7a5f41e2ab04ea9
eb6f10f5452fd08234a524d21df41a6b9be1466c0c3acd39017951cd4122a3cf
ecaa580731d007d7caf61c28102d3bc5daaa3ff63751127cad1e3f9ac06abe0b
ed7adec770601be4ef6b7b823e4ec7f2e6005810d996960c21cca7e8af20839f
efdc406eb4651d150e5b3729c3abd97da3f35c8370f78e45f5c6adef8a93f4be
f0a11eb1d8fabf95360258de73cf1cd91360c3b97c1ba92d7744e5eaa40f49d1
f280c2fc7c6f0c3cdb80160a91bebbdd3fed81bf46a55f5e1689dacffcf3b8e6
f32fb09e3994db82c4d5411fde68cf309d9e637b9a7bc02457192bf1cdc4e4f8
f4442ae282d43f6efc118b7903e05b3cf992507195239ddae6143f8b91342731
f4f4ef3240cbb7a3ff76c04a500ec97afda047be3de676cf4640400bac651773
f5350b0f80f32d5b89efdaf67ca24d790a9960dd1e8bd371f97fb84d3be7d9b0
f5d06911ad2428743c7145836cd0bbe00bc78de44e0bf68637c98ad2dc9cd3fa
f6a9278652be2fb55f6dd5aa3af7b522a0a10dcc8aef682a40ba2bf461b41bdc
f807e579e83fd6daa687a9d7e0a919a8e7300d1a662df012cf5cedd5c8049641
f83b56ef6b6b1b99aa5d9c57d51373408815b1e28a727b35a5f96de0738b9e91
f903a7866ddb2a49d1f4a97bae6f04d4996f5b22bc85ad57ae74bd8911245322
fac2cd7d30dfe3162bda5a424d32221b801dec5a627cdd7bffcd03ba67e6928f
fb8eb817d7251014c136b441bd4004fa6567908059013edbb938925f23b67ceb
fc7764b77d15e6e8d319bbceea046fc891f84213e23f4014c7df21d541bd53f8
fdce77a6d0053f32d231518a84a71bcab5c86045ed52369da00b89d4284aef46
ffb7cdfc96982a0186340d72bfd063b384437bbd34c8b5be3d5f409af0e16d91