
blogfreely.net
104.21.50.83
Public Scan
Open in
urlscan Pro
https://blogfreely.net/ariesmail83/what-lies-beneath-the-reality-of-darknet-marketplaces 8yr old
Submission: On September 05 via manual (September 5th 2025, 12:06:13 pm UTC) from IT — Scanned from TW
Summary
TLS certificate: Issued by WE1 on August 24th 2025. Valid for: 3mo.
This is the only time blogfreely.net was scanned on urlscan.io!
urlscan.io Verdict: No classification
Domain & IP information
| IP Address | AS Autonomous System | ||
|---|---|---|---|
| 7 | 104.21.50.83 104.21.50.83 | 13335 (CLOUDFLAR...) (CLOUDFLARENET) | |
| 1 | 172.64.151.12 172.64.151.12 | 13335 (CLOUDFLAR...) (CLOUDFLARENET) | |
| 8 | 2 |
| Apex Domain Subdomains |
Transfer | |
|---|---|---|
| 7 |
blogfreely.net
blogfreely.net 8yr old |
154 KB |
| 1 |
chainalysis.com
www.chainalysis.com 11yr old |
390 KB |
| 8 | 2 |
| Domain | Requested by | |
|---|---|---|
| 7 | blogfreely.net |
blogfreely.net
|
| 1 | www.chainalysis.com |
blogfreely.net
|
| 8 | 2 |
This site contains links to these domains. Also see Links.
| Domain |
|---|
| mydarknetmarketsonline.com |
| Subject Issuer | Validity | Valid | |
|---|---|---|---|
| blogfreely.net WE1 |
2025-08-24 - 2025-11-22 |
3mo | crt.sh |
| www.chainalysis.com WE1 |
2025-09-02 - 2025-12-01 |
3mo | crt.sh |
This page contains 1 frames:
Primary Page:
https://blogfreely.net/ariesmail83/what-lies-beneath-the-reality-of-darknet-marketplaces
Frame ID: 9160740BD0CA14649D7D594313A96F51
Requests: 8 HTTP requests in this frame

1 Outgoing links
These are links going to different origins than the main page.
Title: darknet sites
Search URL Search Domain Scan URL
Redirected requests
There were HTTP redirect chains for the following requests:
8 HTTP transactions
0 data transactions
| Method Protocol |
Status | Resource Path |
Size x-fer |
Time Latency |
Type MIME-Type |
IP Location |
|||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
|
GET H3 |
200 |
Primary Request
what-lies-beneath-the-reality-of-darknet-marketplaces
Show response
blogfreely.net/ariesmail83/ |
13 KB 5 KB |
413ms
310ms |
Document
text/html |
104.21.50.83 CLOUDFLARENET |
|||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
write.css
blogfreely.net/css/ |
49 KB 11 KB |
97ms
95ms |
Stylesheet
text/css |
104.21.50.83 CLOUDFLARENET |
|||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
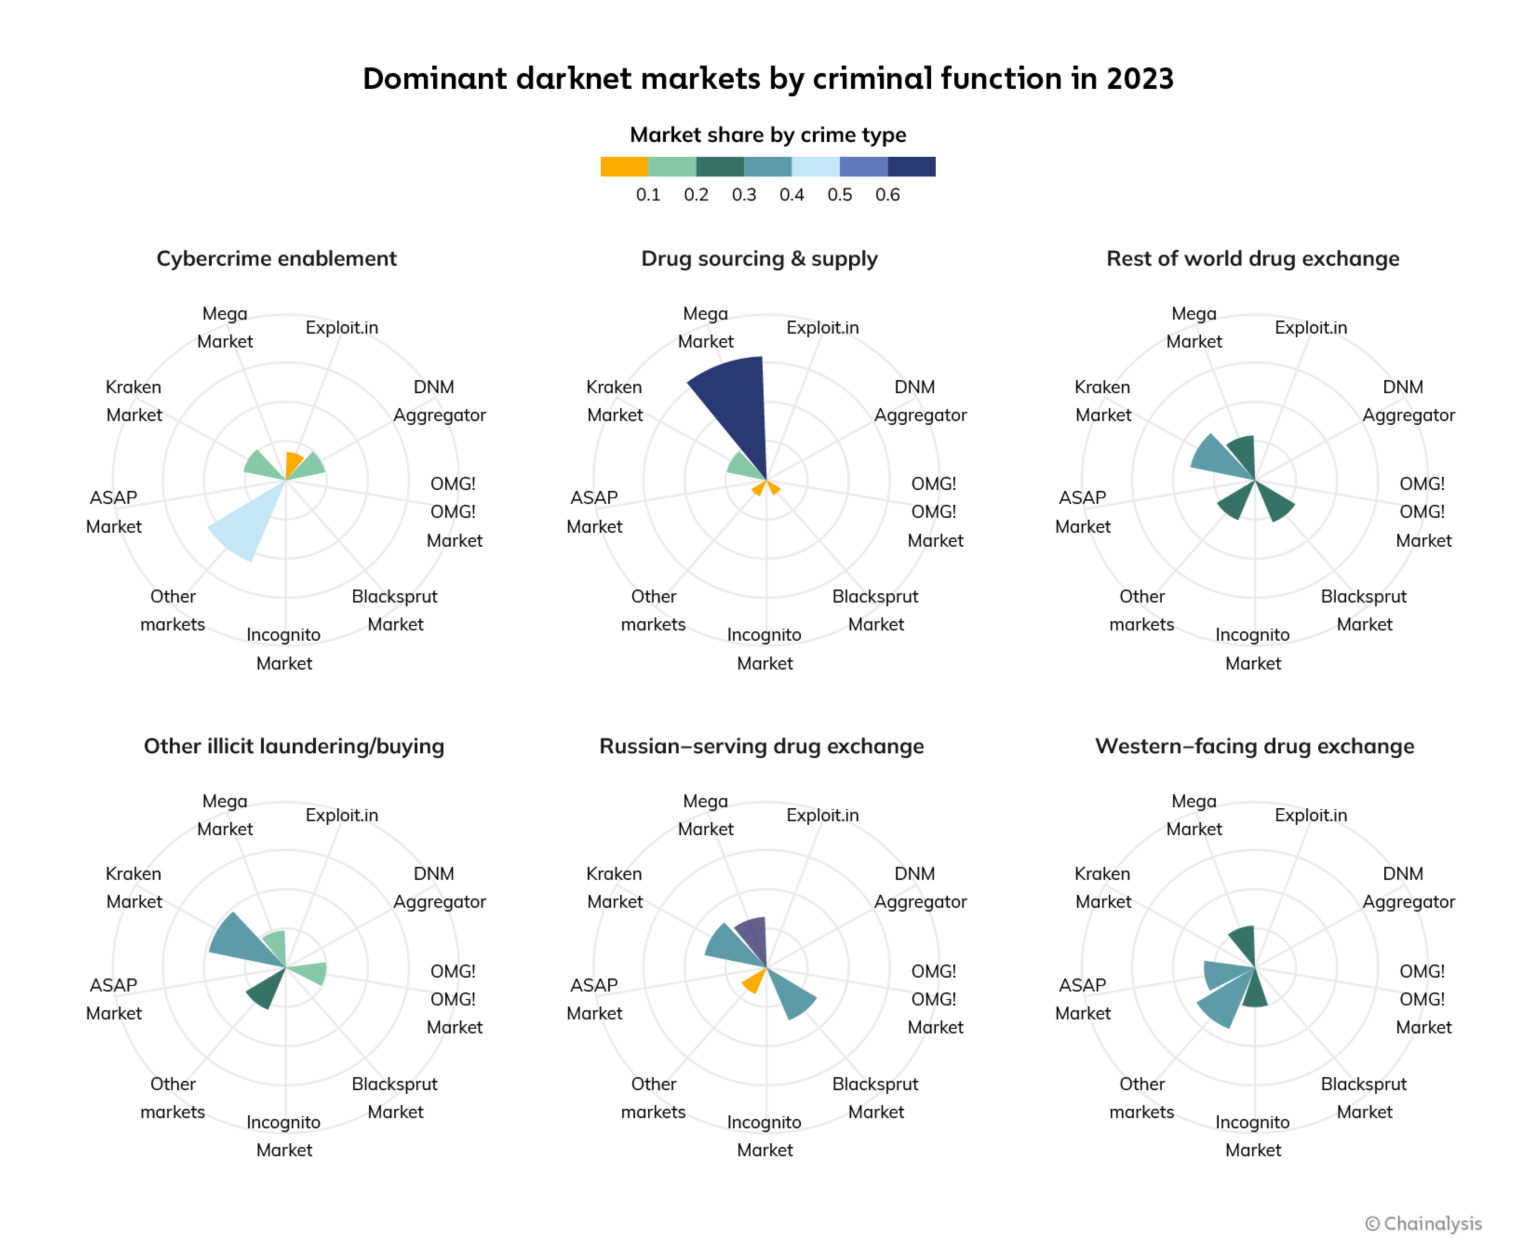
dominant-darknet-markets-by-criminal-function-in-2023-1536x1240.png
www.chainalysis.com/wp-content/uploads/2024/03/ |
390 KB 390 KB |
965ms
848ms |
Image
image/png |
172.64.151.12 CLOUDFLARENET |
|||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
webfont.js
Show response
blogfreely.net/js/ |
12 KB 6 KB |
93ms
93ms |
Script
application/javascript |
104.21.50.83 CLOUDFLARENET |
|||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
fonts.css
blogfreely.net/css/ |
2 KB 817 B |
91ms
91ms |
Stylesheet
text/css |
104.21.50.83 CLOUDFLARENET |
|||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
Lora-Regular.woff2
blogfreely.net/fonts/ |
62 KB 63 KB |
88ms
88ms |
Font
font/woff2 |
104.21.50.83 CLOUDFLARENET |
|||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
Lora-Bold.woff2
blogfreely.net/fonts/ |
67 KB 67 KB |
166ms
166ms |
Font
font/woff2 |
104.21.50.83 CLOUDFLARENET |
|||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
favicon.ico
blogfreely.net/ |
6 KB 1 KB |
90ms
89ms |
Other
image/vnd.microsoft.icon |
104.21.50.83 CLOUDFLARENET |
|||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||


Verdicts & Comments Add Verdict or Comment
3 JavaScript Window variables
These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.
function| unpinPost object| WebFontConfig object| WebFont0 Cookies
Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.
Indicators
This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.
blogfreely.net
www.chainalysis.com
104.21.50.83
172.64.151.12
19194360f69da1a7c5fe2e5e79f5452b3b8cbff371e3a08e95344b3c6aee258a
26ee6f80607aa285386fc2132073fda3639fddfb3c139d7e92490de306d2b8d1
2711b037e078e306e59765e9fc22d9f86867eb26af8c6af72d864a1c52bed8ac
3d0ba3e8fa123cedd468a27d7ffd8f5347bad048d0cb1c5baf29925677d203ed
5aad84fd548b01f6f96d44b6254b68a247e5d12800b5284c72a5310d05746ee5
77b76d49c7c9ea6204b05cfb0c8b006f26793081102bd948b1b41be00c3d4645
8a7be585b1fb4fb1a26b547dd62ef1ae034c5ba42aad471473704a8ac9a9637a
b1119cb35793ecd895e0cd5f1a2894fa14994c703412a9b5c8c229abcdd1ffb8