
www.pp2apk75.cyou
13.32.99.63
Public Scan
Open in
urlscan Pro
http://bit.ly/4gTQBIr 13yr old
Effective URL:
https://www.pp2apk75.cyou/?bnp=grlu&gz=15aayn 2mo old
Submission: On July 24 via manual (July 24th 2026, 5:47:13 am UTC) from IN — Scanned from DE
Summary
TLS certificate: Issued by Amazon RSA 2048 M01 on July 12th 2026. Valid for: 7mo.
This is the only time www.pp2apk75.cyou was scanned on urlscan.io!
urlscan.io Verdict: No classification
Domain & IP information
| IP Address | AS Autonomous System | ||
|---|---|---|---|
| 1 1 | 67.199.248.10 67.199.248.10 | 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC) | |
| 7 | 13.32.99.63 13.32.99.63 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 1 | 157.240.0.6 157.240.0.6 | 32934 (FACEBOOK) (FACEBOOK - Facebook) | |
| 8 | 2 |
ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US)
PTR: bit.ly
| bit.ly 13yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-13-32-99-63.fra60.r.cloudfront.net
| www.pp2apk75.cyou 2mo old |
ASN32934 (FACEBOOK - Facebook, Inc., US)
PTR: xx-fbcdn-shv-02-fra3.fbcdn.net
| connect.facebook.net 13yr old |
| Apex Domain Subdomains |
Transfer | |
|---|---|---|
| 7 |
pp2apk75.cyou
www.pp2apk75.cyou 2mo old |
455 KB |
| 1 |
facebook.net
connect.facebook.net — Cisco Umbrella Rank: 226 13yr old |
103 KB |
| 1 |
bit.ly
1 redirects
bit.ly — Cisco Umbrella Rank: 6506 13yr old |
407 B |
| 8 | 3 |
| Domain | Requested by | |
|---|---|---|
| 7 | www.pp2apk75.cyou |
www.pp2apk75.cyou
|
| 1 | connect.facebook.net |
www.pp2apk75.cyou
|
| 1 | bit.ly | 1 redirects |
| 8 | 3 |
This site contains no links.
| Subject Issuer | Validity | Valid | |
|---|---|---|---|
| pp2apk75.cyou Amazon RSA 2048 M01 |
2026-07-12 - 2027-01-25 |
7mo | crt.sh |
| *.facebook.com DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2026-05-02 - 2026-07-31 |
3mo | crt.sh |
This page contains 1 frames:
Primary Page:
https://www.pp2apk75.cyou/?bnp=grlu&gz=15aayn
Frame ID: 2E35FBED70B980DB636CF24A7564F4BA
Requests: 8 HTTP requests in this frame
Screenshot
Page Title
PP2.COMPage URL History Show full URLs
-
http://bit.ly/4gTQBIr
HTTP 307
https://bit.ly/4gTQBIr HTTP 301
https://www.pp2apk75.cyou/?bnp=grlu&gz=15aayn Page URL
Detected technologies
 Vue.js
(JavaScript frameworks)
Expand
Detected patterns
- <(?!svg)[^>]+\sdata-v(?:ue)?-
 Facebook Pixel
(Analytics)
Expand
Detected patterns
- connect\.facebook\.\w+/.+/fbevents\.js
Page Statistics
0 Outgoing links
These are links going to different origins than the main page.
Page URL History
This captures the URL locations of the websites, including HTTP redirects and client-side redirects via JavaScript or Meta fields.
-
http://bit.ly/4gTQBIr
HTTP 307
https://bit.ly/4gTQBIr HTTP 301
https://www.pp2apk75.cyou/?bnp=grlu&gz=15aayn Page URL
Redirected requests
There were HTTP redirect chains for the following requests:
8 HTTP transactions
0 data transactions
| Method Protocol |
Status | Resource Path |
Size x-fer |
Time Latency |
Type MIME-Type |
IP Location |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
|
GET H2 |
200 |
Primary Request
/
Show response
www.pp2apk75.cyou/ Redirect Chain
|
2 KB 1 KB |
80ms
15ms |
Document
text/html |
13.32.99.63 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
index-LvBxwxMg.js
Show response
www.pp2apk75.cyou/assets/ |
108 KB 109 KB |
36ms
35ms |
Script
application/javascript |
13.32.99.63 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
index-wPDa672U.css
www.pp2apk75.cyou/assets/ |
2 KB 3 KB |
29ms
29ms |
Stylesheet
text/css |
13.32.99.63 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
fbevents.js
Show response
connect.facebook.net/en_US/ |
388 KB 103 KB |
25ms
8ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
data.json
Show response
www.pp2apk75.cyou/grlu/ |
545 B 858 B |
11ms
11ms |
Fetch
application/json |
13.32.99.63 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
loading.jpeg
www.pp2apk75.cyou/grlu/ |
327 KB 327 KB |
11ms
11ms |
Image
image/jpeg |
13.32.99.63 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
top_header.jpeg
www.pp2apk75.cyou/grlu/ |
10 KB 10 KB |
11ms
11ms |
Image
image/jpeg |
13.32.99.63 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
favicon-ByCePhUV.ico
www.pp2apk75.cyou/assets/ |
4 KB 4 KB |
15ms
15ms |
Other
image/x-icon |
13.32.99.63 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||


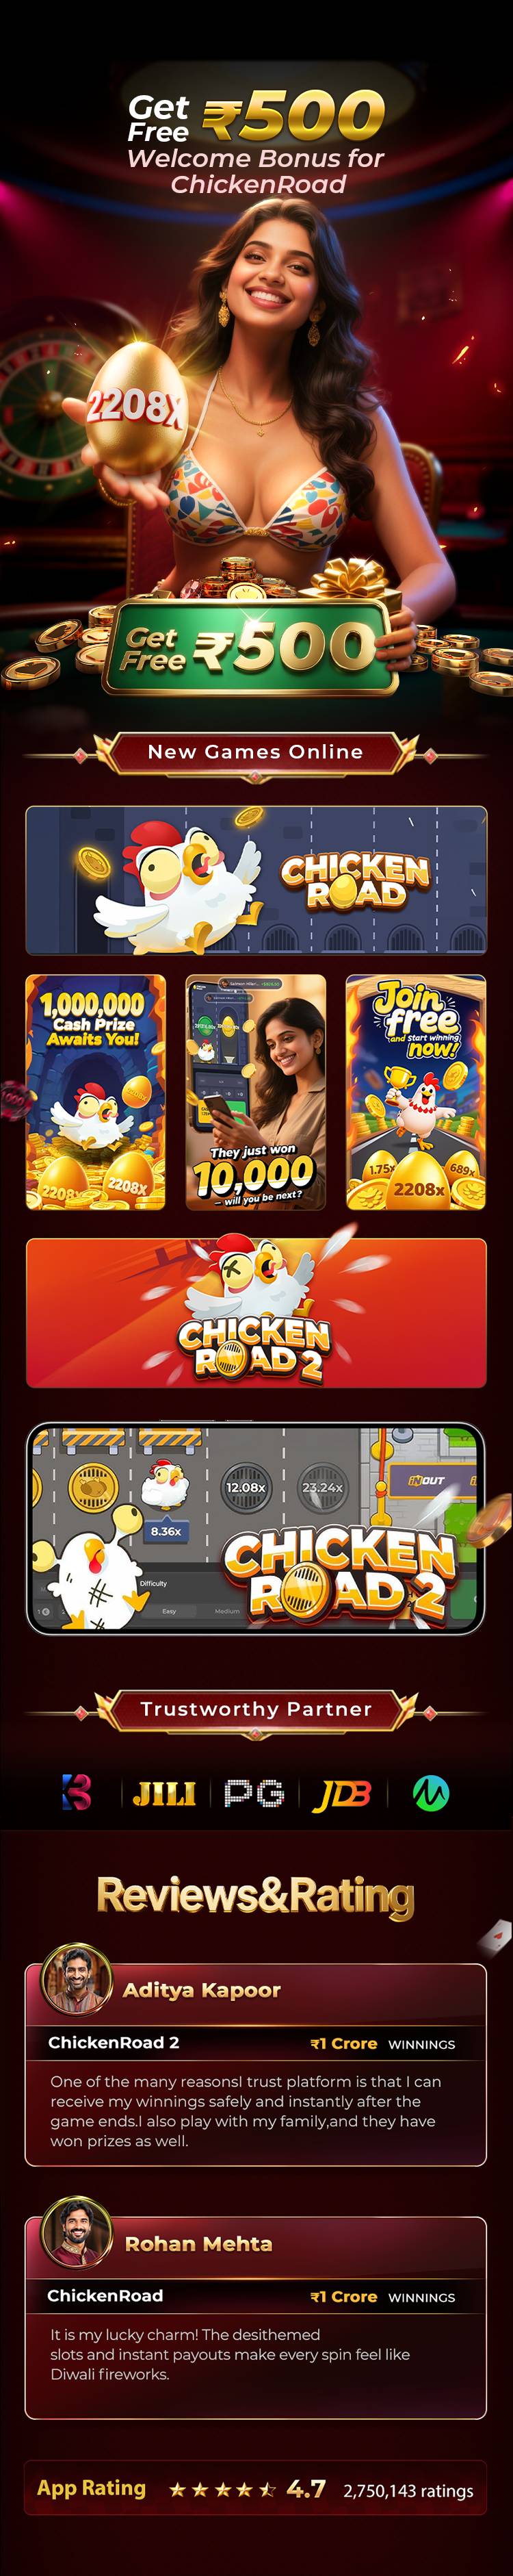


Verdicts & Comments Add Verdict or Comment
6 JavaScript Window variables
These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.
object| __VUE_INSTANCE_SETTERS__ object| __VUE_SSR_SETTERS__ object| AF_SMART_SCRIPT function| fbq function| _fbq boolean| __VUE__1 Cookies
Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.
| Domain/Path | Expires | Name / Value | |||
|---|---|---|---|---|---|
| .bit.ly/ | 1970-01-21 20:07:04 |
Name: _bit Value: q6o5Ld-edf521cd588c9b1c3e-00M |
Indicators
This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.
bit.ly
connect.facebook.net
www.pp2apk75.cyou
13.32.99.63
157.240.0.6
67.199.248.10
08ebad1806b786ca817bad259d2e061e1f38211726eb47ef3f6f484bf980253b
25159ebaf83bb3cf42c0580a34c4f33f19987f5d5da393af6528f9dd61e49ee4
8eb14f05b4be162fc6e259f919b396b3e94482fb7fa334985ece165a30a76541
a114d475c258e218f5027dcb07ad15d176cd61c2b78e19d05c87dd8be33b9231
bda83d88e4e1b2c00bc55f47b182b9a1c6e70b6714c54ddda4fddf939c06dcb9
bff9b26f6808e3519677833aaf245c86ebe7af792a9d3ebef203016ce80170f1
d04bc58c22eb939432ae468dde0b1b36a12fb10491a4c8bffb335175a9a1fb4a
d966c786adc51e495d4672a9b9023d66c563e0505080760ecfdec7b72a78e44c