
www.bleepingcomputer.com
172.66.135.165
Public Scan
Open in
urlscan Pro
https://www.bleepingcomputer.com/news/security/google-says-chrome-cuts-7-billion-unwanted-android-notifications-a-day-to-fight-ab... 10yr old
Submission: On August 12 via api (August 12th 2026, 3:24:06 am UTC) from PL — Scanned from PT
Summary
TLS certificate: Issued by Sectigo Public Server Authentication ... on April 14th 2026. Valid for: 7mo.
This is the only time www.bleepingcomputer.com was scanned on urlscan.io!
urlscan.io Verdict: No classification
Domain & IP information
| IP Address | AS Autonomous System | ||
|---|---|---|---|
| 1 | 172.66.135.165 172.66.135.165 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 192.178.183.95 192.178.183.95 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 39 | 104.26.13.6 104.26.13.6 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 5 | 104.20.18.126 104.20.18.126 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 192.178.183.97 192.178.183.97 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 2 4 | 142.251.154.119 142.251.154.119 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 3 | 142.251.14.157 142.251.14.157 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 142.251.110.94 142.251.110.94 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 34.160.152.31 34.160.152.31 | 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC) | |
| 1 | 104.18.18.98 104.18.18.98 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 11 | 3.160.150.117 3.160.150.117 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 2 | 136.69.42.170 136.69.42.170 | 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC) | |
| 4 | 142.251.13.155 142.251.13.155 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 216.239.34.36 216.239.34.36 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 142.251.127.154 142.251.127.154 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 142.250.154.94 142.250.154.94 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 3.77.161.124 3.77.161.124 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 2 | 63.184.140.131 63.184.140.131 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 78 | 19 |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| www.bleepingcomputer.com 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: lcfraw-in-f95.1e100.net
| fonts.googleapis.com 10yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| www.bleepstatic.com 9yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| a.pub.network 9yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: lcfraw-in-f97.1e100.net
| www.googletagmanager.com 13yr old |
ASN15169 (GOOGLE - Google LLC, US)
| www.google.com 13yr old | |
| www.gstatic.com 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: pm-in-f157.1e100.net
| pagead2.googlesyndication.com 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: bz-in-f94.1e100.net
| fonts.gstatic.com 10yr old |
ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US)
PTR: 31.152.160.34.bc.googleusercontent.com
| d.pub.network 9yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| edge.cdn-vitals.com 7mo old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-3-160-150-117.fra60.r.cloudfront.net
| cmp.inmobi.com 3yr old |
ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US)
PTR: 170.42.69.136.bc.googleusercontent.com
| c.pub.network 9yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: wt-in-f155.1e100.net
| securepubads.g.doubleclick.net 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
| region1.analytics.google.com 5yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: lcfrai-in-f154.1e100.net
| stats.g.doubleclick.net 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: bt-in-f94.1e100.net
| www.google.pt 10yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: ec2-3-77-161-124.eu-central-1.compute.amazonaws.com
| visit-server.inmobi-choice.io 2yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: ec2-63-184-140-131.eu-central-1.compute.amazonaws.com
| api.cmp.inmobi.com 3yr old |
| Apex Domain Subdomains |
Transfer | |
|---|---|---|
| 39 |
bleepstatic.com
www.bleepstatic.com — Cisco Umbrella Rank: 189098 9yr old |
1 MB |
| 13 |
inmobi.com
cmp.inmobi.com — Cisco Umbrella Rank: 6859 3yr old api.cmp.inmobi.com — Cisco Umbrella Rank: 23537 3yr old |
345 KB |
| 8 |
pub.network
a.pub.network — Cisco Umbrella Rank: 5989 9yr old d.pub.network — Cisco Umbrella Rank: 6552 9yr old c.pub.network — Cisco Umbrella Rank: 6103 9yr old |
421 KB |
| 5 |
doubleclick.net
securepubads.g.doubleclick.net — Cisco Umbrella Rank: 335 10yr old stats.g.doubleclick.net — Cisco Umbrella Rank: 183 10yr old |
261 KB |
| 3 |
googlesyndication.com
pagead2.googlesyndication.com — Cisco Umbrella Rank: 141 10yr old |
221 KB |
| 3 |
gstatic.com
www.gstatic.com — Cisco Umbrella Rank: 9 10yr old fonts.gstatic.com — Cisco Umbrella Rank: 44 10yr old |
48 KB |
| 3 |
google.com
2 redirects
www.google.com — Cisco Umbrella Rank: 3 13yr old region1.analytics.google.com — Cisco Umbrella Rank: 3939 5yr old |
19 B |
| 1 |
inmobi-choice.io
visit-server.inmobi-choice.io — Cisco Umbrella Rank: 10378 2yr old |
|
| 1 |
google.pt
www.google.pt — Cisco Umbrella Rank: 61791 10yr old |
408 B |
| 1 |
cdn-vitals.com
edge.cdn-vitals.com — Cisco Umbrella Rank: 8317 7mo old |
|
| 1 |
googletagmanager.com
www.googletagmanager.com — Cisco Umbrella Rank: 59 13yr old |
181 KB |
| 1 |
googleapis.com
fonts.googleapis.com — Cisco Umbrella Rank: 67 10yr old |
2 KB |
| 1 |
bleepingcomputer.com
www.bleepingcomputer.com — Cisco Umbrella Rank: 161934 10yr old |
18 KB |
| 78 | 13 |
| Domain | Requested by | |
|---|---|---|
| 39 | www.bleepstatic.com |
www.bleepingcomputer.com
www.bleepstatic.com |
| 11 | cmp.inmobi.com |
www.bleepstatic.com
cmp.inmobi.com |
| 5 | a.pub.network |
www.bleepingcomputer.com
a.pub.network |
| 4 | securepubads.g.doubleclick.net |
a.pub.network
securepubads.g.doubleclick.net www.bleepingcomputer.com |
| 3 | pagead2.googlesyndication.com |
www.bleepingcomputer.com
pagead2.googlesyndication.com |
| 2 | api.cmp.inmobi.com |
cmp.inmobi.com
|
| 2 | c.pub.network |
a.pub.network
|
| 2 | www.gstatic.com |
www.bleepingcomputer.com
|
| 2 | www.google.com | 2 redirects |
| 1 | visit-server.inmobi-choice.io |
cmp.inmobi.com
|
| 1 | www.google.pt |
www.bleepingcomputer.com
|
| 1 | stats.g.doubleclick.net |
www.googletagmanager.com
|
| 1 | region1.analytics.google.com |
www.googletagmanager.com
|
| 1 | edge.cdn-vitals.com |
a.pub.network
|
| 1 | d.pub.network |
www.bleepingcomputer.com
|
| 1 | fonts.gstatic.com |
fonts.googleapis.com
|
| 1 | www.googletagmanager.com |
www.bleepingcomputer.com
|
| 1 | fonts.googleapis.com |
www.bleepingcomputer.com
|
| 1 | www.bleepingcomputer.com | |
| 78 | 19 |
This site contains links to these domains. Also see Links.
| Subject Issuer | Validity | Valid | |
|---|---|---|---|
| bleepingcomputer.com Sectigo Public Server Authentication CA DV R36 |
2026-04-14 - 2026-10-29 |
7mo | crt.sh |
| upload.video.google.com WE2 |
2026-07-20 - 2026-10-12 |
3mo | crt.sh |
| bleepstatic.com WE1 |
2026-06-21 - 2026-09-19 |
3mo | crt.sh |
| pub.network WE1 |
2026-06-29 - 2026-09-27 |
3mo | crt.sh |
| *.google-analytics.com WE2 |
2026-07-20 - 2026-10-12 |
3mo | crt.sh |
| *.g.doubleclick.net WE2 |
2026-07-20 - 2026-10-12 |
3mo | crt.sh |
| *.gstatic.com WE2 |
2026-07-20 - 2026-10-12 |
3mo | crt.sh |
| d.pub.network WR3 |
2026-07-13 - 2026-10-11 |
3mo | crt.sh |
| cdn-vitals.com WE1 |
2026-07-20 - 2026-10-18 |
3mo | crt.sh |
| cmp.inmobi.com Sectigo Public Server Authentication CA OV E36 |
2026-06-26 - 2027-01-10 |
7mo | crt.sh |
| c.pub.network SSL.com TLS Issuing RSA CA R1 |
2026-08-04 - 2027-02-18 |
7mo | crt.sh |
| *.google.pt WR2 |
2026-07-20 - 2026-10-12 |
3mo | crt.sh |
| visit-server.inmobi-choice.io Amazon RSA 2048 M04 |
2026-04-14 - 2026-10-28 |
7mo | crt.sh |
This page contains 1 frames:
Primary Page:
https://www.bleepingcomputer.com/news/security/google-says-chrome-cuts-7-billion-unwanted-android-notifications-a-day-to-fight-abuse/
Frame ID: E076445992E11E259E11E7DDE310D846
Requests: 78 HTTP requests in this frame
Screenshot
Page Title
Google says Chrome cuts 7 billion unwanted Android notifications a day to fight abuseDetected technologies
 Bootstrap
(UI frameworks)
Expand
Detected patterns
- <link[^>]* href=[^>]*?bootstrap(?:[^>]*?([0-9a-fA-F]{7,40}|[\d]+(?:.[\d]+(?:.[\d]+)?)?)|)[^>-]*?(?:\.min)?\.css
- (?:/|-)bootstrap(?:[^/]*?([0-9a-fA-F]{7,40}|[\d]+(?:\.[\d]+(?:\.[\d]+)?)?)|)[^/]*?(?:\.min)?\.js
 AMP
(JavaScript frameworks)
Expand
Detected patterns
- <link rel="amphtml"
 DoubleClick Floodlight
(Advertising)
Expand
Detected patterns
- \.doubleclick\.net
 FancyBox
(JavaScript libraries)
Expand
Detected patterns
- jquery\.fancybox(?:\.pack|\.min)?\.js(?:\?v=([\d.]+))?$
 Font Awesome
(Font scripts)
Expand
Detected patterns
- (?:F|f)o(?:n|r)t-?(?:A|a)wesome(?:.*?([0-9a-fA-F]{7,40}|[\d]+(?:.[\d]+(?:.[\d]+)?)?)|)
 Google AdSense
(Advertising)
Expand
Detected patterns
- googlesyndication\.com/
 Google Analytics
(Analytics)
Expand
Detected patterns
- googletagmanager\.com/gtag/js
 Google Publisher Tag
(Advertising)
Expand
Detected patterns
- securepubads\.g\.doubleclick.net/tag/js/gpt\.js
 Google Tag Manager
(Tag managers)
Expand
Detected patterns
- \.googletagmanager\.com/
 jQuery
(JavaScript libraries)
Expand
Detected patterns
- jquery
- /jquery(?:-(\d+\.\d+\.\d+))[/.-]
jQuery Migrate
(JavaScript libraries)
Expand
Detected patterns
- jquery-migrate(?:\.min)?(?:-?((?:\d+\.)+\d+))?(?:\.min)?\.js
 Prebid
(Advertising)
Expand
Detected patterns
- /prebid\.js
Page Statistics
20 Outgoing links
These are links going to different origins than the main page.
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Title: Deals
Search URL Search Domain Scan URL
Title: eLearning
Search URL Search Domain Scan URL
Title: IT Certification Courses
Search URL Search Domain Scan URL
Title: Gear + Gadgets
Search URL Search Domain Scan URL
Title: Security
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Title: blog post
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Title: Webinar: Shadow AI in 2026 (and how attackers are taking advantage)
Search URL Search Domain Scan URL
Title: See how Skyhigh Security's patent-pending approach secures every browser session without costly and clunky enterprise browser replacements.
Search URL Search Domain Scan URL
Title: Pixellot discovered and secured hundreds of unmanaged AI agent identities in weeks, not months. Download the case study for how.
Search URL Search Domain Scan URL
Title: See how real inboxes, fake stores and AI scams shaped H1 2026 cyber threats
Search URL Search Domain Scan URL
Title: Overdue a password health-check? Audit your Active Directory for free
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Redirected requests
There were HTTP redirect chains for the following requests:
Request Chain 13- https://www.google.com/coop/cse/brand?form=cse-search-box&lang=en HTTP 301
- https://www.gstatic.com/prose/brandjs.js
- https://www.google.com/coop/cse/brand?form=cse-search-box&lang=en HTTP 301
- https://www.gstatic.com/prose/brandjs.js
78 HTTP transactions
1 data transactions
| Method Protocol |
Status | Resource Path |
Size x-fer |
Time Latency |
Type MIME-Type |
IP Location |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
|
GET H2 |
200 |
Primary Request
/
Show response
www.bleepingcomputer.com/news/security/google-says-chrome-cuts-7-billion-unwanted-android-notifications-a-day-to-fight-abuse/ |
87 KB 18 KB |
658ms
553ms |
Document
text/html |
172.66.135.165 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
css
fonts.googleapis.com/ |
33 KB 2 KB |
269ms
95ms |
Stylesheet
text/css |
192.178.183.95 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
bootstrap.min.css
www.bleepstatic.com/js/redesign/bootstrap/css/ |
119 KB 18 KB |
171ms
64ms |
Stylesheet
text/css |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
main.css
www.bleepstatic.com/css/redesign/ |
65 KB 11 KB |
160ms
53ms |
Stylesheet
text/css |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
home.css
www.bleepstatic.com/css/redesign/ |
15 KB 3 KB |
228ms
120ms |
Stylesheet
text/css |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
news.css
www.bleepstatic.com/css/redesign/ |
36 KB 6 KB |
231ms
124ms |
Stylesheet
text/css |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
jquery-3.5.1.min.js
Show response
www.bleepstatic.com/js/redesign/ |
87 KB 30 KB |
241ms
134ms |
Script
text/javascript |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
jquery-migrate-1.4.1.min.js
Show response
www.bleepstatic.com/js/redesign/ |
10 KB 4 KB |
221ms
114ms |
Script
text/javascript |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
news.js
Show response
www.bleepstatic.com/js/redesign/ |
247 B 416 B |
103ms
101ms |
Script
text/javascript |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
cls.css
a.pub.network/bleepingcomputer-com/ |
4 KB 1 KB |
123ms
66ms |
Stylesheet
text/css |
104.20.18.126 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
pubfig.min.js
Show response
a.pub.network/bleepingcomputer-com/ |
76 KB 30 KB |
53ms
51ms |
Script
application/javascript |
104.20.18.126 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
qc-consent.js
Show response
www.bleepstatic.com/js/qc-consent/ |
9 KB 3 KB |
102ms
100ms |
Script
text/javascript |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
js
Show response
www.googletagmanager.com/gtag/ |
548 KB 181 KB |
293ms
116ms |
Script
application/javascript |
192.178.183.97 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
logo.png
www.bleepstatic.com/images/site/ |
1 KB 2 KB |
106ms
104ms |
Image
image/webp |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
brandjs.js
Show response
www.gstatic.com/prose/ Redirect Chain
|
14 KB 6 KB |
56ms
56ms |
Script
text/javascript |
142.251.154.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
t-claude-boundaries-970.jpg
www.bleepstatic.com/c/t/ |
65 KB 66 KB |
141ms
140ms |
Image
image/jpeg |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Google.jpg
www.bleepstatic.com/content/hl-images/2025/09/02/ |
290 KB 291 KB |
285ms
285ms |
Image
image/jpeg |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
w-AITR-Playbook.jpg
www.bleepstatic.com/c/w/ |
83 KB 83 KB |
73ms
69ms |
Image
image/jpeg |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Chrome-notifications-feature.png
www.bleepstatic.com/images/news/u/1097497/Google/ |
261 KB 262 KB |
231ms
228ms |
Image
image/png |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
adsbygoogle.js
Show response
pagead2.googlesyndication.com/pagead/js/ |
161 KB 56 KB |
199ms
102ms |
Script
text/javascript |
142.251.14.157 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
t-even-claude-boundaries-400.jpg
www.bleepstatic.com/c/t/ |
64 KB 64 KB |
54ms
51ms |
Image
image/jpeg |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
material-400.jpg
www.bleepstatic.com/c/m/ |
71 KB 71 KB |
110ms
108ms |
Image
image/jpeg |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
twitter.png
www.bleepstatic.com/images/site/login/ |
282 B 624 B |
110ms
108ms |
Image
image/webp |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
bootstrap.js
Show response
www.bleepstatic.com/js/redesign/bootstrap/js/ |
74 KB 15 KB |
124ms
123ms |
Script
text/javascript |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
blazy.min.js
Show response
www.bleepstatic.com/js/blazy/ |
5 KB 2 KB |
99ms
97ms |
Script
text/javascript |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
bleep.js
Show response
www.bleepstatic.com/js/redesign/ |
4 KB 1 KB |
101ms
100ms |
Script
text/javascript |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
jquery.fancybox.js
Show response
www.bleepstatic.com/js/redesign/fancybox/ |
48 KB 13 KB |
103ms
102ms |
Script
text/javascript |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
fixto.min.js
Show response
www.bleepstatic.com/js/fixto/ |
8 KB 3 KB |
101ms
98ms |
Script
text/javascript |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
brandjs.js
Show response
www.gstatic.com/prose/ Redirect Chain
|
14 KB 0 |
57ms
57ms |
Script
text/javascript |
142.251.154.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET DATA |
200 OK |
truncated
/ |
37 B 0 |
Image
image/gif |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
material-400.jpg
www.bleepstatic.com/c/m/ |
71 KB 0 |
114ms
114ms |
Image
image/jpeg |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
login_bg.png
www.bleepstatic.com/images/site/ |
126 B 412 B |
129ms
129ms |
Image
image/webp |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
nav_bg.png
www.bleepstatic.com/images/site/ |
83 B 453 B |
126ms
126ms |
Image
image/png |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
calendar.png
www.bleepstatic.com/images/site/ |
86 B 382 B |
106ms
106ms |
Image
image/webp |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
clock.png
www.bleepstatic.com/images/site/ |
252 B 686 B |
127ms
127ms |
Image
image/webp |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
comment-light.png
www.bleepstatic.com/images/site/ |
94 B 447 B |
131ms
130ms |
Image
image/webp |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
32x32-printer.png
www.bleepstatic.com/images/site/ |
258 B 577 B |
126ms
126ms |
Image
image/webp |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
908394e185e9468cda6838ff2129df21.jpg
www.bleepstatic.com/author/photos/ |
20 KB 20 KB |
131ms
131ms |
Image
image/jpeg |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
h4-bg.png
www.bleepstatic.com/images/site/ |
38 B 431 B |
132ms
132ms |
Image
image/webp |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
KFO7CnqEu92Fr1ME7kSn66aGLdTylUAMa3yUBA.woff2
fonts.gstatic.com/s/roboto/v51/ |
42 KB 42 KB |
175ms
83ms |
Font
font/woff2 |
142.251.110.94 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
configs
d.pub.network/v2/sites/bleepingcomputer-com/ |
120 KB 12 KB |
200ms
82ms |
Other
application/json |
34.160.152.31 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
HEAD H3 |
200 |
1.png
a.pub.network/core/imgs/ |
0 0 |
99ms
52ms |
Fetch
image/png |
104.20.18.126 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
HEAD H2 |
204 |
px
edge.cdn-vitals.com/ |
0 0 |
155ms
52ms |
Fetch
|
104.18.18.98 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
jquery.fancybox.css
www.bleepstatic.com/js/redesign/fancybox/ |
5 KB 2 KB |
56ms
51ms |
Stylesheet
text/css |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
fontawesome.min.css
www.bleepstatic.com/redesign/fontawesome6/css/ |
79 KB 17 KB |
56ms
51ms |
Stylesheet
text/css |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
brands.min.css
www.bleepstatic.com/redesign/fontawesome6/css/ |
18 KB 5 KB |
55ms
49ms |
Stylesheet
text/css |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
solid.min.css
www.bleepstatic.com/redesign/fontawesome6/css/ |
572 B 590 B |
58ms
53ms |
Stylesheet
text/css |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
292x176_box.jpg
www.bleepstatic.com/content/hl-images/2026/05/19/thumb/ |
46 KB 47 KB |
59ms
54ms |
Image
image/jpeg |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
choice.js
Show response
cmp.inmobi.com/choice/sktb670LZWvFX/www.bleepingcomputer.com/ |
6 KB 3 KB |
300ms
88ms |
Script
application/javascript |
3.160.150.117 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
fa-solid-900.woff2
www.bleepstatic.com/redesign/fontawesome6/webfonts/ |
147 KB 147 KB |
292ms
193ms |
Font
application/octet-stream |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
fa-brands-400.woff2
www.bleepstatic.com/redesign/fontawesome6/webfonts/ |
105 KB 105 KB |
156ms
57ms |
Font
application/octet-stream |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
OPTIONS H2 |
200 |
c
c.pub.network/v2/ |
0 0 |
194ms
75ms |
Preflight
|
136.69.42.170 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
c
Show response
c.pub.network/v2/ |
36 B 109 B |
77ms
75ms |
Fetch
text/plain |
136.69.42.170 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
prebid.js
Show response
a.pub.network/bleepingcomputer-com/ |
569 KB 194 KB |
62ms
62ms |
Script
application/javascript |
104.20.18.126 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
gpt.js
Show response
securepubads.g.doubleclick.net/tag/js/ |
121 KB 36 KB |
202ms
102ms |
Script
text/javascript |
142.251.13.155 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
pubfig.engine.js
Show response
a.pub.network/bleepingcomputer-com/ |
598 KB 185 KB |
52ms
52ms |
Script
application/javascript |
104.20.18.126 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
abg_config
Show response
pagead2.googlesyndication.com/getconfig/ |
3 B 30 B |
168ms
167ms |
Fetch
application/json |
142.251.14.157 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
show_ads_impl_fy2021.js
Show response
pagead2.googlesyndication.com/pagead/managed/js/adsense/m202608060101/ |
505 KB 165 KB |
82ms
82ms |
Script
text/javascript |
142.251.14.157 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
cmp2.js
Show response
cmp.inmobi.com/tcfv2/58/ |
491 KB 112 KB |
104ms
104ms |
Script
application/javascript |
3.160.150.117 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
collect
region1.analytics.google.com/g/ |
0 0 |
207ms
75ms |
Fetch
text/plain |
216.239.34.36 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
collect
stats.g.doubleclick.net/g/ |
0 564 B |
277ms
93ms |
Ping
text/plain |
142.251.127.154 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
ga-audiences
www.google.pt/ads/ |
42 B 408 B |
217ms
81ms |
Image
image/gif |
142.250.154.94 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
pubads_impl.js
Show response
securepubads.g.doubleclick.net/pagead/managed/js/gpt/m202608070101/ |
643 KB 201 KB |
84ms
84ms |
Script
text/javascript |
142.251.13.155 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
ppub_config
Show response
securepubads.g.doubleclick.net/pagead/ |
1 KB 516 B |
111ms
110ms |
Fetch
application/json |
142.251.13.155 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
gpt
securepubads.g.doubleclick.net/pagead/managed/dict/m202608110101/ |
64 KB 23 KB |
89ms
89ms |
Other
text/plain |
142.251.13.155 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
geoip
Show response
cmp.inmobi.com/ |
47 B 330 B |
264ms
89ms |
XHR
application/json |
3.160.150.117 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
bleeping.ico
www.bleepstatic.com/favicon/ |
8 KB 9 KB |
53ms
52ms |
Other
application/octet-stream |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
vendor-list-trimmed-v1.json
Show response
cmp.inmobi.com/GVL-v3/ |
709 KB 77 KB |
107ms
107ms |
XHR
application/json |
3.160.150.117 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
cmp-list.json
Show response
cmp.inmobi.com/GVL-v2/ |
29 KB 6 KB |
91ms
90ms |
XHR
application/json |
3.160.150.117 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
cmp2ui-en.js
Show response
cmp.inmobi.com/tcfv2/58/ |
467 KB 104 KB |
89ms
89ms |
Script
application/javascript |
3.160.150.117 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
visit-event
visit-server.inmobi-choice.io/ |
0 0 |
283ms
92ms |
Ping
application/json |
3.77.161.124 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
purposes-national-en.json
Show response
cmp.inmobi.com/us-mspa/v1/ |
10 KB 2 KB |
89ms
88ms |
XHR
application/json |
3.160.150.117 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
vendor-list-trimmed-v1.json
Show response
cmp.inmobi.com/GVL-v3/ |
709 KB 0 |
0ms
0ms |
XHR
application/json |
3.160.150.117 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
google-atp-list.json
Show response
cmp.inmobi.com/tcfv2/ |
171 KB 39 KB |
95ms
94ms |
XHR
application/json |
3.160.150.117 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
purposes-en.json
Show response
cmp.inmobi.com/google-basic-consent/v1/ |
3 KB 1 KB |
105ms
104ms |
XHR
application/json |
3.160.150.117 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
/
Show response
api.cmp.inmobi.com/ |
2 B 100 B |
353ms
92ms |
XHR
text/plain |
63.184.140.131 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
/
Show response
api.cmp.inmobi.com/ |
2 B 101 B |
352ms
91ms |
XHR
text/plain |
63.184.140.131 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
geoip
Show response
cmp.inmobi.com/ |
47 B 329 B |
89ms
89ms |
XHR
application/json |
3.160.150.117 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
bleeping-computerlogo-lg.png
www.bleepstatic.com/logos/ |
7 KB 7 KB |
52ms
52ms |
Image
image/webp |
104.26.13.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||








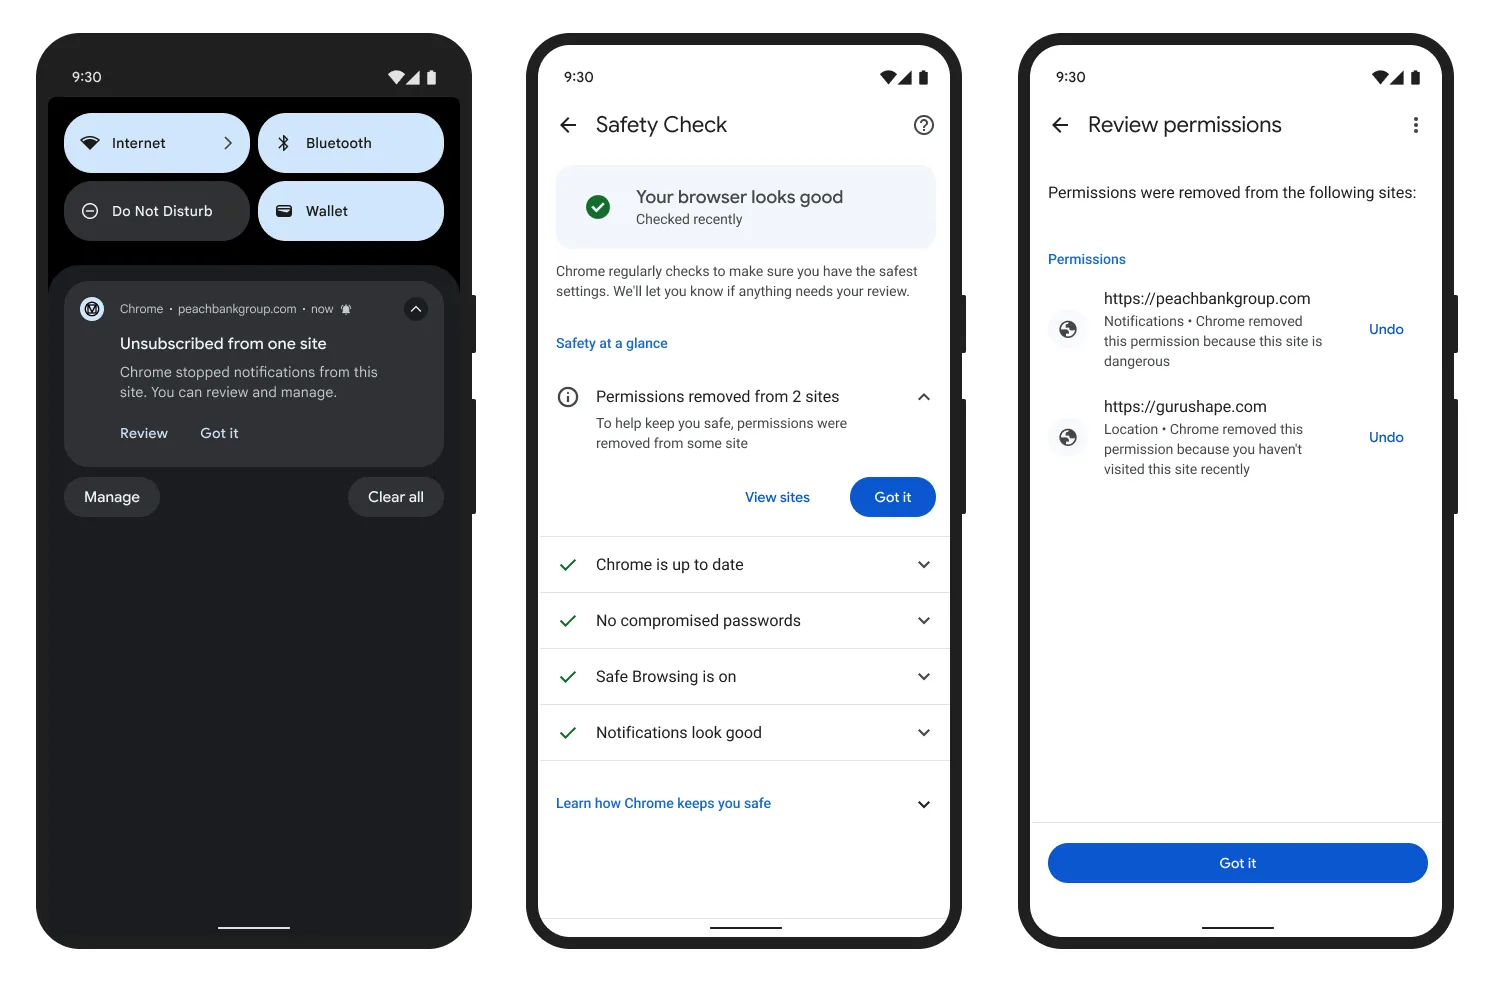






Verdicts & Comments Add Verdict or Comment
56 JavaScript Window variables
These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.
object| 0 object| 1 object| 2 function| $ function| jQuery object| freestar function| gtag object| dataLayer object| adsbygoogle object| _pubfigInstanceManagerConfig function| Blazy object| fixto function| validate_comment_box_not_empty function| cz_strip_tags function| cz_br2nl function| editForm string| loginhash boolean| main_nav_hide_flag function| call_main_nav_hide function| loadDeferredStyles function| raf function| __tcfapi function| __gpp_addFrame function| __gpp_stub function| __gpp_msghandler function| __gpp function| __uspapi object| googletag object| fsprebid object| google_js_reporting_queue number| google_srt boolean| BGtEY object| google_logging_queue object| ggeac object| google_persistent_state_async object| google_tag_data object| google_reactive_ads_global_state object| google_ad_modifications object| google_sa_queue function| google_process_slots boolean| google_apltlad number| google_unique_id object| fqjyf number| google_rum_task_id_counter string| google_user_agent_client_hint object| fsprebidChunk object| _pbjsGlobals object| mnet object| google_tag_manager function| onYouTubeIframeAPIReady object| gaGlobal function| google_sa_impl boolean| googFloatingToolbarManagerAsyncPositionUpdate object| regeneratorRuntime function| __tcfapiui function| __gbcapi6 Cookies
Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.
| Domain/Path | Expires | Name / Value | |||
|---|---|---|---|---|---|
| .bleepingcomputer.com/ | 1969-12-31 23:59:59 |
Name: session_id Value: ff42ae41de27011fa7f5a6448cac3281 |
|||
| www.bleepingcomputer.com/ | 1969-12-31 23:59:59 |
Name: PHPSESSID Value: 3789b7d56a543be7d05b17c0abc1877e |
|||
| www.bleepingcomputer.com/ | 1970-01-21 16:58:17 |
Name: lav Value: 26587 |
|||
| .bleepingcomputer.com/ | 1970-01-22 01:51:05 |
Name: _ga_GD465VRQLD Value: GS2.1.s1786505048$o1$g0$t1786505048$j60$l0$h0 |
|||
| .bleepingcomputer.com/ | 1970-01-22 01:51:05 |
Name: _ga Value: GA1.1.992470486.1786505048 |
|||
| .www.bleepingcomputer.com/ | 1970-01-22 01:36:41 |
Name: usprivacy Value: 1--- |
Security Headers
This page lists any security headers set by the main page. If you want to understand what these mean and how to use them, head on over to this page
| Header | Value |
|---|---|
| Content-Security-Policy | upgrade-insecure-requests; frame-ancestors 'self' |
| X-Frame-Options | SAMEORIGIN |
Indicators
This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.
a.pub.network
api.cmp.inmobi.com
c.pub.network
cmp.inmobi.com
d.pub.network
edge.cdn-vitals.com
fonts.googleapis.com
fonts.gstatic.com
pagead2.googlesyndication.com
region1.analytics.google.com
securepubads.g.doubleclick.net
stats.g.doubleclick.net
visit-server.inmobi-choice.io
www.bleepingcomputer.com
www.bleepstatic.com
www.google.com
www.google.pt
www.googletagmanager.com
www.gstatic.com
104.18.18.98
104.20.18.126
104.26.13.6
136.69.42.170
142.250.154.94
142.251.110.94
142.251.127.154
142.251.13.155
142.251.14.157
142.251.154.119
172.66.135.165
192.178.183.95
192.178.183.97
216.239.34.36
3.160.150.117
3.77.161.124
34.160.152.31
63.184.140.131
0233185a19290ef50b30c8b42b9fa43ee8d868767e9cbca36da2b9f832daee34
040d62b356ce3b603ecaa2ef11ca2c601f87e43a0ba1ba361aed80de9be36dc8
080a9ed428559ef602668b4c00f114f1a11c3f6b02a435f0bdc154578e4d7f22
0eb8eedb0b77263616c3baf378c98930ad3ed3e6494ef9300ae8358981ce6374
0f427d0f88a0698c955ff63bf13af4ca80c9b32f218b5e210847450da901a74f
1404ca348bd75ef836f4dd8b6f2cc719458642d1237c368296b2fc652dca47dc
14b88e905a2d72905aa5141d6d50fce5b2ce73f2c89c407d2e4db192b7404511
19db4a2cde712e2ceaac317e732b4ec40b62818a938a8bf8391ad68470845019
316e33bfe6ab63fbb1920bfcf23774c4a779aa22c0707c7831064f9a1bb87c43
32e73e8e0eec3e6c1345d84e7ef091b90e71fb0045814043b34c914156235eb9
351f30131b4c9c04c66cf701e7a31cb13f6f6c5ef00b689d2456fddbe270f5e2
3ae24b9fae4398a4ecd9155e643bc043c5770f85ea9b00e9b7bff672dda24911
3fe890d088ecf0cc9bc1b9069201e52972dbad6237865524090e15982d0de718
48eb8b500ae6a38617b5738d2b3faec481922a7782246e31d2755c034a45cd5d
4f932a516afac94f925bd5ea2baf92773d218283055c4b2f0d56b04074bf5788
565339bc4d33d72817b583024112eb7f5cdf3e5eef0252d6ec1b9c9a94e12bb3
57b59ca705037e9fa948ecbc290feb04fbbb2d3e99bbd46def0a5cd4e720e599
5bd13de5418d361e992959a02b7b85c938e90a7a806b09c91843413a93944c12
60f8976fbc9e2aff02580b307d1e7dc2c5a7dd8a801bb9398bf153438b852975
6395e6f9f6fbcd953f0ffa40615094c565d86c265fb5028e64dd2dc872b5ce69
67d86a29de7993fbd23b7dde2c4f26bdc434055c35a4b08c830c0d02fcfa6dd2
6c78ce6b6d1928630b903084ea9d503643f303ba05455860cc7cd17f7687cc65
6d92dfc1700fd38cd130ad818e23bc8aef697f815b2ea5face2b5dfad22f2e11
6f809cfb9f0da72e26ca8c20696314252a7943a9af43d0fde3b2da7188b78d9b
788f791ffbe7737aacce97f0500d347300df31b731ff6024da3d2563dbce8016
7945a016863643f7dcba9d9052700f792f2aa7573773c1e54e75ad796e5f0697
7a5d218c8e40dc33b9a0c27b49c2a5d0c9696ea53ee6371882d348a31116ae9b
7d6d26827b887aa09b2a5eb7c001e35b93773e53c36ddbfc127ad824e0a6ba39
8434675120acc0e4718865e12b7744c9d1b616fdcf73356da64dd83fb450d2e1
85ae9534729617e69eafa40195c7854697eb3d13b4205f3ee467e07c4af0a24b
863ab50a39fc203ca8f614cef14c6cc700ee64bfeacd41426dce9ef8cbd98509
91b8e81022f91c23d7025e997c3de187ad3c125205ee4a150c447a4c04e911e2
942935ead42820e6c9184f099c77dde34fa4be70d395a17c47b5d7ad07967339
968a8e56e4adaf8c135199ebd7f6cc065424ca45974d4dfbeb5607e69fe72fcd
9b00bc7eeaebea9218e372fcf87b33f9f3c125fdf7f779c6a937fdb316dab4a7
9ca1d8648cbf1f6b12c863bbd7bf560b35888eda8b7845117e833974d3e7ec44
9cdb6bfef8d4212d9bf634ca6724a28e85dfa69cd404e6f9d3760d70a7873949
a3265d09b7308c6191659688d9b8ecf4a1e0171d0f8113d065b6383183fbf15f
a7e925f6192a3f7907621f9dde8afc47752d671d4a796f2cd5a53cfbc07c214b
aaa8307a875df311b5265e93c7cca738002a533ae25cd7ea159dca0ecc2f4d1f
ac27f4c1072b8611c66d022aa70a5b77dbad58b0f9e792f1d9c3f25f0728e60f
ac828bd7813b937db3fc9e1366df83f95951ca9241a1167dfb8aa05c296d7ba9
adb66fdd8f898f54ce5d73fd6c442dbf5ed00ae4b70c99b48ab79b540af669f2
b6d60e97440882efefe201f2155b4db2557363535281b4ab241b5b27bd6bf387
b76cbc969c7c82e75c421e174224d789946300b96001ad530ccf22d630779aa9
bac85e662bff5e8d94bea12a289d12303c46f0d2d0cf4ba25e8feb1ea8ac5996
bb229a48bee31f5d54ca12dc9bd960c63a671f0d4be86a054c1d324a44499d96
bd8912141a9de225fc520c2ed08e471ed4ff6d6b543ac8d6fe6a9666b4154f11
bea0853c66075c7f57ec59a8e1659628ba1142c809a324e12319823e05610bc3
c492ba8669f9c264c2a5cbe5f2d8c69036c82f167b0fe3dd3902ab7b84689685
c6f48b7af3e0d1e90c8360fa6325ded938c0b0c9b5e30c34c19f924e6c1046c4
c8fac3a2c9653cbdf20b8e1deccf13dce8ad300f41cbc53c1bf73b166ec61575
cbae144c316aa2b382e3c93e54f1e11eab21faf8d349cce30e358be6c54cbcfb
cfac05f501d6d4d62e29fff1049569c3c2aa8732af8db3a36e8fa252f05f5861
d27bc752105c079f8a516e9142406a9fc12cbb409f9bf8681f2ddfe0360b52a6
d31bb928796de63263d24849cefbc824ffd08dbc0c5a700e7ec5b5612ae19af0
d53b46a7c3137c6377c8add2b7bfe2663d4383f9deacda35eb4f73b5072d4313
d6d408ceb31cfae3d3d87971b82e522a331aa2eb042a793223b7ec19e419c564
da8caf23d6e1da5cd6fc5b96bff9f6d8f856cd2bb42f5eb3975a7bbddfaf477d
dbd2a35e72edc7d6bde483481a912f1c38aa57fab2747d9b071d317339ee03a2
ded8ccc0bf2159ddbcda148611365dd27ddbca253518d5a939a6b9159263416e
e0d430f575e07a8bac568ce6a0d99b932e47d747ac17c9e8b993d8c87d69f19e
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
e5e67647bb3c355f4a2da0c482d912611676b7751002703d69f3cd521de748ab
e746e5c91b415a31c16795776b127d1abc864c5edc54fb835ab4708f40a4ceaa
e9b6ae8e83441e6327875efe55ec419c47a0ead44f9c17f483722b43de7abb1f
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
efe527cf424c7710e87f51d6fe0cff69843ba1a5af5e939f04eda7a8ac76e8b8
f7f6a5894f1d19ddad6fa392b2ece2c5e578cbf7da4ea805b6885eb6985b6e3d