
enford.cic.com.jo
2606:4700::6810:1d0e
Public Scan
Open in
urlscan Pro
http://enford.cic.com.jo/ 9yr old
Effective URL:
https://enford.cic.com.jo/ 9yr old
Submission: On August 14 via api (August 14th 2026, 11:14:09 am UTC) from US — Scanned from DE Go Pro
Only in urlscan Pro
- Select different country locations for Private Scans.
- Use a global network of additional scanning locations and residential IPs for scanning.
- Interact with pages while you are scanning them.
- Download files from remote websites.
- Scan websites on the Tor Network.
Summary
TLS certificate: Issued by WR1 on August 13th 2026. Valid for: 3mo.
This is the only time enford.cic.com.jo was scanned on urlscan.io!
urlscan.io Verdict: No classification
Domain & IP information
| IP Address | AS Autonomous System | ||
|---|---|---|---|
| 8 | 2606:4700::68... 2606:4700::6810:1d0e | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 21 | 2606:4700::68... 2606:4700::6812:451 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 3 | 2a02:26f0:350... 2a02:26f0:3500:587::1e80 | 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.) | |
| 1 | 2606:4700::68... 2606:4700::6810:4f49 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 3 | 52.19.120.20 52.19.120.20 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 5 | 2a00:1450:400... 2a00:1450:4001:c1f::66 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 2a04:4e42:400... 2a04:4e42:400::411 | 54113 (FASTLY) (FASTLY - Fastly) | |
| 1 | 52.30.167.93 52.30.167.93 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 2 | 63.140.62.210 63.140.62.210 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 1 1 | 18.202.72.190 18.202.72.190 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 3 | 2a00:1450:400... 2a00:1450:4001:c17::61 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 3 | 2001:4860:480... 2001:4860:4802:34::36 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 50 | 11 |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| enford.cic.com.jo 9yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| resources.dealer-asset.co 5yr old | |
| live.dealer-asset.co 8yr old |
ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL)
| assets.adobedtm.com 13yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| static.cloudflareinsights.com 7yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: ec2-52-19-120-20.eu-west-1.compute.amazonaws.com
| dpm.demdex.net 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
| img.youtube.com 10yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: ec2-52-30-167-93.eu-west-1.compute.amazonaws.com
| geronimo.demdex.net 4yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: ip-63-140-62-210.data.adobedc.net
| geronimo.d3.sc.omtrdc.net 9yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: ec2-18-202-72-190.eu-west-1.compute.amazonaws.com
| cm.everesttech.net 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
| www.googletagmanager.com 14yr old |
ASN15169 (GOOGLE - Google LLC, US)
| region1.google-analytics.com 5yr old |
| Apex Domain Subdomains |
Transfer | |
|---|---|---|
| 21 |
dealer-asset.co
resources.dealer-asset.co 5yr old live.dealer-asset.co — Cisco Umbrella Rank: 811813 8yr old |
1 MB |
| 8 |
cic.com.jo
enford.cic.com.jo 9yr old |
134 KB |
| 5 |
youtube.com
img.youtube.com — Cisco Umbrella Rank: 1311 10yr old |
74 KB |
| 4 |
demdex.net
1 redirects
dpm.demdex.net — Cisco Umbrella Rank: 358 10yr old geronimo.demdex.net 4yr old |
6 KB |
| 3 |
google-analytics.com
region1.google-analytics.com — Cisco Umbrella Rank: 4010 5yr old |
|
| 3 |
googletagmanager.com
www.googletagmanager.com — Cisco Umbrella Rank: 59 14yr old |
479 KB |
| 3 |
adobedtm.com
assets.adobedtm.com — Cisco Umbrella Rank: 266 13yr old |
65 KB |
| 2 |
omtrdc.net
geronimo.d3.sc.omtrdc.net 9yr old |
492 B |
| 1 |
everesttech.net
1 redirects
cm.everesttech.net — Cisco Umbrella Rank: 1802 10yr old |
490 B |
| 1 |
jquery.com
code.jquery.com — Cisco Umbrella Rank: 810 13yr old |
31 KB |
| 1 |
cloudflareinsights.com
static.cloudflareinsights.com — Cisco Umbrella Rank: 316 7yr old |
11 KB |
| 50 | 11 |
| Domain | Requested by | |
|---|---|---|
| 15 | live.dealer-asset.co |
enford.cic.com.jo
|
| 8 | enford.cic.com.jo |
enford.cic.com.jo
resources.dealer-asset.co static.cloudflareinsights.com code.jquery.com |
| 6 | resources.dealer-asset.co |
enford.cic.com.jo
resources.dealer-asset.co |
| 5 | img.youtube.com | |
| 3 | region1.google-analytics.com |
www.googletagmanager.com
|
| 3 | www.googletagmanager.com |
resources.dealer-asset.co
www.googletagmanager.com |
| 3 | dpm.demdex.net |
1 redirects
enford.cic.com.jo
|
| 3 | assets.adobedtm.com |
enford.cic.com.jo
assets.adobedtm.com |
| 2 | geronimo.d3.sc.omtrdc.net |
assets.adobedtm.com
|
| 1 | cm.everesttech.net | 1 redirects |
| 1 | geronimo.demdex.net |
assets.adobedtm.com
|
| 1 | code.jquery.com |
live.dealer-asset.co
|
| 1 | static.cloudflareinsights.com |
enford.cic.com.jo
|
| 50 | 13 |
This site contains links to these domains. Also see Links.
| Domain |
|---|
| maps.google.com |
| www.facebook.com |
| www.youtube.com |
| www.me.ford.com |
| www.izmo.ai |
| www.youtube-nocookie.com |
| Subject Issuer | Validity | Valid | |
|---|---|---|---|
| enford.cic.com.jo WR1 |
2026-08-13 - 2026-11-11 |
3mo | crt.sh |
| dealer-asset.co WE1 |
2026-08-06 - 2026-11-04 |
3mo | crt.sh |
| assets.adobedtm.com DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2026-06-15 - 2026-12-30 |
7mo | crt.sh |
| cloudflareinsights.com WE1 |
2026-08-14 - 2026-11-12 |
3mo | crt.sh |
| *.google.com WE2 |
2026-07-20 - 2026-10-12 |
3mo | crt.sh |
| *.jquery.com Sectigo Public Server Authentication CA DV E36 |
2026-05-20 - 2026-12-04 |
7mo | crt.sh |
| *.demdex.com DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2025-10-14 - 2026-11-14 |
1yr | crt.sh |
| *.d3.sc.omtrdc.net DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2026-02-11 - 2027-03-14 |
1yr | crt.sh |
| *.google-analytics.com WE2 |
2026-07-20 - 2026-10-12 |
3mo | crt.sh |
This page contains 7 frames:
Primary Page:
https://enford.cic.com.jo/
Frame ID: 8AC9FE1D349797CD855A60820DA0A1CD
Requests: 44 HTTP requests in this frame
Frame:
https://img.youtube.com/vi/I3vDc7okaj4/hqdefault.jpg
Frame ID: 45EFA342442BFA552B1BDEA2664288FA
Requests: 1 HTTP requests in this frame
Frame:
https://img.youtube.com/vi/pyL4pKvNH2I/hqdefault.jpg
Frame ID: EC93ABB17BE70A38FFAFC931453D5536
Requests: 1 HTTP requests in this frame
Frame:
https://img.youtube.com/vi/rZmmyKiOEOc/hqdefault.jpg
Frame ID: 73BBFE8B332DD9C170F6DA362057ED1F
Requests: 1 HTTP requests in this frame
Frame:
https://img.youtube.com/vi/4mLH0G7VsJA/hqdefault.jpg
Frame ID: 8C96D619FCCDB554BADFAAF308876F2A
Requests: 1 HTTP requests in this frame
Frame:
https://img.youtube.com/vi/J3X10c-PB8I/hqdefault.jpg
Frame ID: AA5454297A01A0806B4B8FC2CF450388
Requests: 1 HTTP requests in this frame
Frame:
https://geronimo.demdex.net/dest5.html?d_nsid=0
Frame ID: E6FEF20FF20AF8354B429A6CBAAF1028
Requests: 1 HTTP requests in this frame
Screenshot
Go Pro
Only in urlscan Pro
Use the Visual Search feature to find pages with visually similar screenshots.
Click for more information
Free trials of urlscan Pro are available.
Page Title
Welcome to Ford JordanPage URL History
Go Pro
Only in urlscan Pro
Search our real-time database of newly observed domains and
hostnames. Pivot on different attributes, and setup keyword alerts for
newly observed domains.
Click for more information
Free trials of urlscan Pro are available.
Show full URLs
-
http://enford.cic.com.jo/
HTTP 307
https://enford.cic.com.jo/ Page URL
Detected technologies
 YouTube
(Video players)
Expand
Detected patterns
- \.youtube\.com/
 Adobe Audience Manager
(Segmentation)
Expand
Detected patterns
 Cloudflare Browser Insights
(Analytics)
Expand
Detected patterns
- static\.cloudflareinsights\.com/beacon(?:\.min)?\.js
 Google Analytics
(Analytics)
Expand
Detected patterns
- googletagmanager\.com/gtag/js
 Google Tag Manager
(Tag managers)
Expand
Detected patterns
- \.googletagmanager\.com/
 jQuery
(JavaScript libraries)
Expand
Detected patterns
- jquery
- /jquery(?:-(\d+\.\d+\.\d+))[/.-]
jQuery CDN
(CDN)
Expand
Detected patterns
- code\.jquery\.com/
Page Statistics
15 Outgoing links
Go Pro
Only in urlscan Pro
Effortlessly use any on-page link as a pivot to discover other pages pointing to the exact same destination. Seamlessly trace both specific URLs and broader domains to uncover hidden connection networks and map out backlink relationships with ease.
Click for more information
Free trials of urlscan Pro are available.
These are links going to different origins than the main page.
Title: Get directions - This link opens in a new browser tab Get directions - This link opens in a new browser tab
Search URL Search Domain Scan URL
Title: Get directions - This link opens in a new browser tab Get directions - This link opens in a new browser tab
Search URL Search Domain Scan URL
Title: Get directions - This link opens in a new browser tab Get directions - This link opens in a new browser tab
Search URL Search Domain Scan URL
Title: Get directions - This link opens in a new browser tab Get directions - This link opens in a new browser tab
Search URL Search Domain Scan URL
Title: Get directions - This link opens in a new browser tab Get directions - This link opens in a new browser tab
Search URL Search Domain Scan URL
Title: Get directions - This link opens in a new browser tab Get directions - This link opens in a new browser tab
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Title: izmo Holdings UK Ltd
Search URL Search Domain Scan URL
Title: ►
Search URL Search Domain Scan URL
Title: ►
Search URL Search Domain Scan URL
Title: ►
Search URL Search Domain Scan URL
Title: ►
Search URL Search Domain Scan URL
Title: ►
Search URL Search Domain Scan URL
Page URL History
This captures the URL locations of the websites, including HTTP redirects and client-side redirects via JavaScript or Meta fields.
-
http://enford.cic.com.jo/
HTTP 307
https://enford.cic.com.jo/ Page URL
Redirected requests
There were HTTP redirect chains for the following requests:
Request Chain 11- https://dpm.demdex.net/id?d_visid_ver=5.5.0&d_fieldgroup=MC&d_rtbd=json&d_ver=2&d_verify=1&d_orgid=A11A079F574E92AE7F000101%40AdobeOrg&d_nsid=0&ts=1786706049593 HTTP 302
- https://dpm.demdex.net/id/rd?d_visid_ver=5.5.0&d_fieldgroup=MC&d_rtbd=json&d_ver=2&d_verify=1&d_orgid=A11A079F574E92AE7F000101%40AdobeOrg&d_nsid=0&ts=1786706049593
- https://cm.everesttech.net/cm/dd?d_uuid=79083802867410717251866598289228212820 HTTP 302
- https://dpm.demdex.net/ibs:dpid=411&dpuuid=an74gQAAABfdCgMR
50 HTTP transactions
Go Pro
Only in urlscan Pro
Inspect WebSocket connections, examine POST data effortlessly, and track overlap counts in real time. Features live search and filtering across all HTTP output, complete with full response metadata for deep analysis.
Click for more information
Free trials of urlscan Pro are available.
0 data transactions
| Method Protocol |
Status | Resource Path |
Size x-fer |
Time Latency |
Type MIME-Type |
IP Location |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
|
GET H2 |
200 |
Primary Request
/
Show response
enford.cic.com.jo/ Redirect Chain
|
184 KB 21 KB |
109ms
42ms |
Document
text/html |
2606:4700::6810:1d0e Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
index.css
resources.dealer-asset.co/themes/fmlds/latest/ |
294 KB 38 KB |
85ms
45ms |
Stylesheet
text/css |
2606:4700::6812:451 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
analytics.min.js
Show response
live.dealer-asset.co/globalscripts/ |
25 KB 5 KB |
57ms
25ms |
Script
text/javascript |
2606:4700::6812:451 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
launch-93e2457ee5e1.min.js
Show response
assets.adobedtm.com/2ac28aa462b0/355ce071a373/ |
192 KB 51 KB |
54ms
14ms |
Script
application/x-javascript |
2a02:26f0:3500:587::1e80 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
CIClogo2-01.png
live.dealer-asset.co/me1470/dealerlogo/ |
8 KB 8 KB |
56ms
24ms |
Image
image/png |
2606:4700::6812:451 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
snippet-ford.css
live.dealer-asset.co/globalscripts/ |
27 KB 10 KB |
54ms
23ms |
Stylesheet
text/css |
2606:4700::6812:451 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
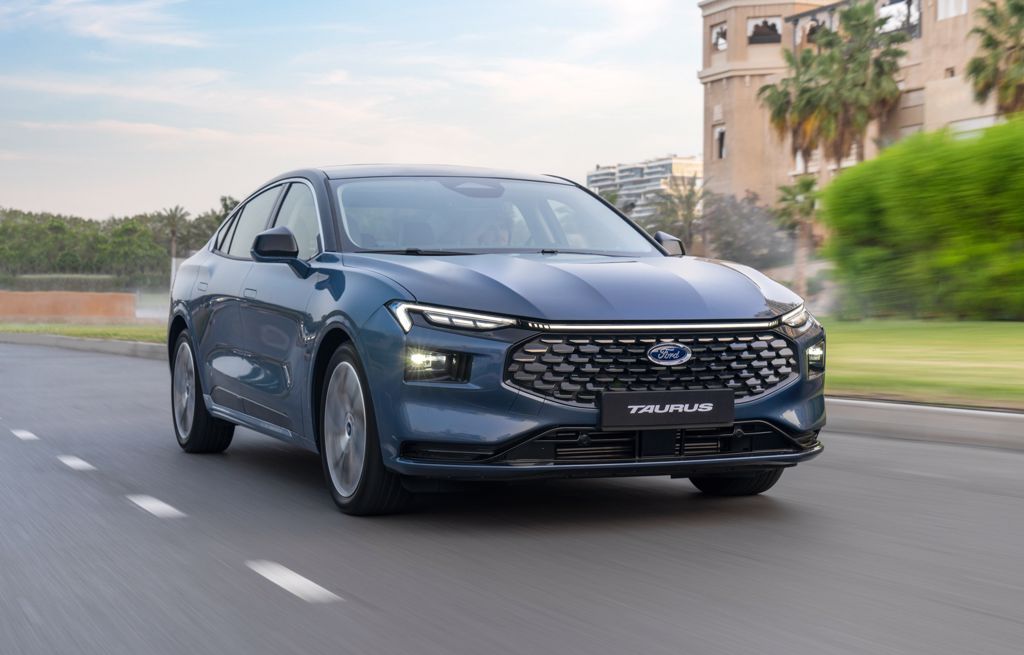
ford-jordan-midel-east-taurus.jpg
live.dealer-asset.co/me1470/siteassets/ |
78 KB 78 KB |
18ms
17ms |
Image
image/jpeg |
2606:4700::6812:451 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
ford-jordan-accesories.jpg
live.dealer-asset.co/me1470/siteassets/ |
76 KB 76 KB |
27ms
27ms |
Image
image/jpeg |
2606:4700::6812:451 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
email-decode.min.js
Show response
enford.cic.com.jo/cdn-cgi/scripts/5c5dd728/cloudflare-static/ |
1 KB 731 B |
15ms
14ms |
Script
application/javascript |
2606:4700::6810:1d0e Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
scripts.min.js
Show response
live.dealer-asset.co/globalscripts/ |
1 KB 824 B |
77ms
77ms |
Script
text/javascript |
2606:4700::6812:451 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
index.js
Show response
resources.dealer-asset.co/themes/fmlds/latest/ |
108 KB 26 KB |
93ms
34ms |
Script
application/javascript |
2606:4700::6812:451 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
v4513226cdae34746b4dedf0b4dfa099e1781791509496
Show response
static.cloudflareinsights.com/beacon.min.js/ |
31 KB 11 KB |
49ms
32ms |
Script
text/javascript |
2606:4700::6810:4f49 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
rd
Show response
dpm.demdex.net/id/ Redirect Chain
|
367 B 912 B |
29ms
29ms |
XHR
application/json |
52.19.120.20 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
AppMeasurement.min.js
Show response
assets.adobedtm.com/extensions/EPbf7b42aa08bc4f10879b1484195e80d1/ |
34 KB 12 KB |
17ms
16ms |
Script
application/x-javascript |
2a02:26f0:3500:587::1e80 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
AppMeasurement_Module_ActivityMap.min.js
Show response
assets.adobedtm.com/extensions/EPbf7b42aa08bc4f10879b1484195e80d1/ |
3 KB 2 KB |
18ms
18ms |
Script
application/x-javascript |
2a02:26f0:3500:587::1e80 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
/
enford.cic.com.jo/ProxyRequest/theme-resources/ |
452 KB 110 KB |
33ms
33ms |
Other
image/svg+xml |
2606:4700::6810:1d0e Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
hqdefault.jpg
img.youtube.com/vi/I3vDc7okaj4/ Frame 45EF |
9 KB 10 KB |
144ms
53ms |
Image
image/jpeg |
2a00:1450:4001:c1f::66 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
hqdefault.jpg
img.youtube.com/vi/pyL4pKvNH2I/ Frame EC93 |
11 KB 11 KB |
203ms
115ms |
Image
image/jpeg |
2a00:1450:4001:c1f::66 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
hqdefault.jpg
img.youtube.com/vi/rZmmyKiOEOc/ Frame 73BB |
25 KB 25 KB |
145ms
58ms |
Image
image/jpeg |
2a00:1450:4001:c1f::66 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
FordF-1-Regular.57e86fc0.woff2
resources.dealer-asset.co/themes/fmlds/latest/ |
39 KB 39 KB |
20ms
20ms |
Font
font/woff2 |
2606:4700::6812:451 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
FordF-1-Semibold.b8e2a0be.woff2
resources.dealer-asset.co/themes/fmlds/latest/ |
40 KB 40 KB |
18ms
18ms |
Font
font/woff2 |
2606:4700::6812:451 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
FordF-1-Bold.89e90e5f.woff2
resources.dealer-asset.co/themes/fmlds/latest/ |
38 KB 38 KB |
57ms
57ms |
Font
font/woff2 |
2606:4700::6812:451 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
hqdefault.jpg
img.youtube.com/vi/4mLH0G7VsJA/ Frame 8C96 |
20 KB 20 KB |
170ms
95ms |
Image
image/jpeg |
2a00:1450:4001:c1f::66 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
FordSignatureLogo-2024.png
live.dealer-asset.co/me21/websiteasset/ |
11 KB 11 KB |
72ms
71ms |
Image
image/png |
2606:4700::6812:451 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
B3444R.jpg
live.dealer-asset.co/images/me1470/banners/ |
296 KB 296 KB |
45ms
44ms |
Image
image/jpeg |
2606:4700::6812:451 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
B3445R.jpg
live.dealer-asset.co/images/me1470/banners/ |
122 KB 123 KB |
47ms
46ms |
Image
image/jpeg |
2606:4700::6812:451 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
ford-jordan-f150.jpg
live.dealer-asset.co/me1470/siteassets/ |
144 KB 145 KB |
22ms
22ms |
Image
image/jpeg |
2606:4700::6812:451 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
ford-jordan-taurus.jpg
live.dealer-asset.co/me1470/siteassets/ |
74 KB 74 KB |
21ms
20ms |
Image
image/jpeg |
2606:4700::6812:451 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
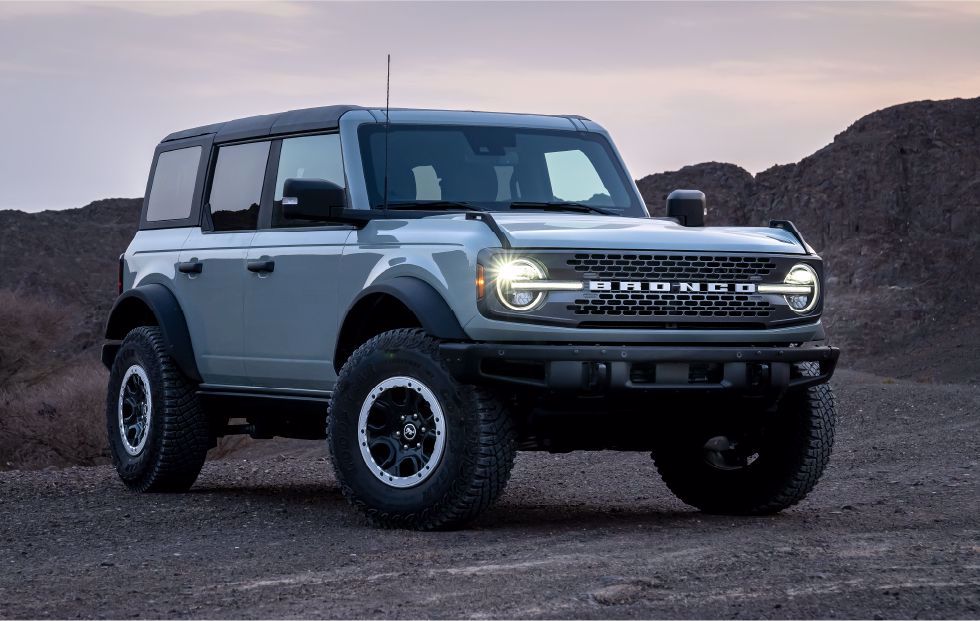
ford-jordan-bronco.jpg
live.dealer-asset.co/me1470/siteassets/ |
99 KB 99 KB |
25ms
25ms |
Image
image/jpeg |
2606:4700::6812:451 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
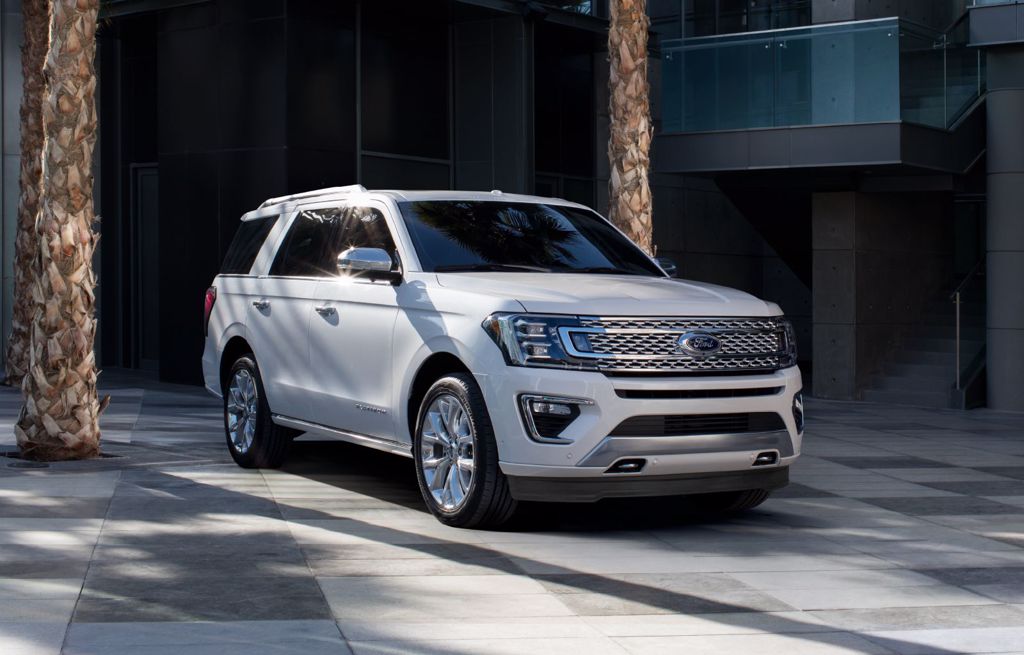
ford-jordan-expedition.jpg
live.dealer-asset.co/me1470/siteassets/ |
90 KB 90 KB |
26ms
25ms |
Image
image/jpeg |
2606:4700::6812:451 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
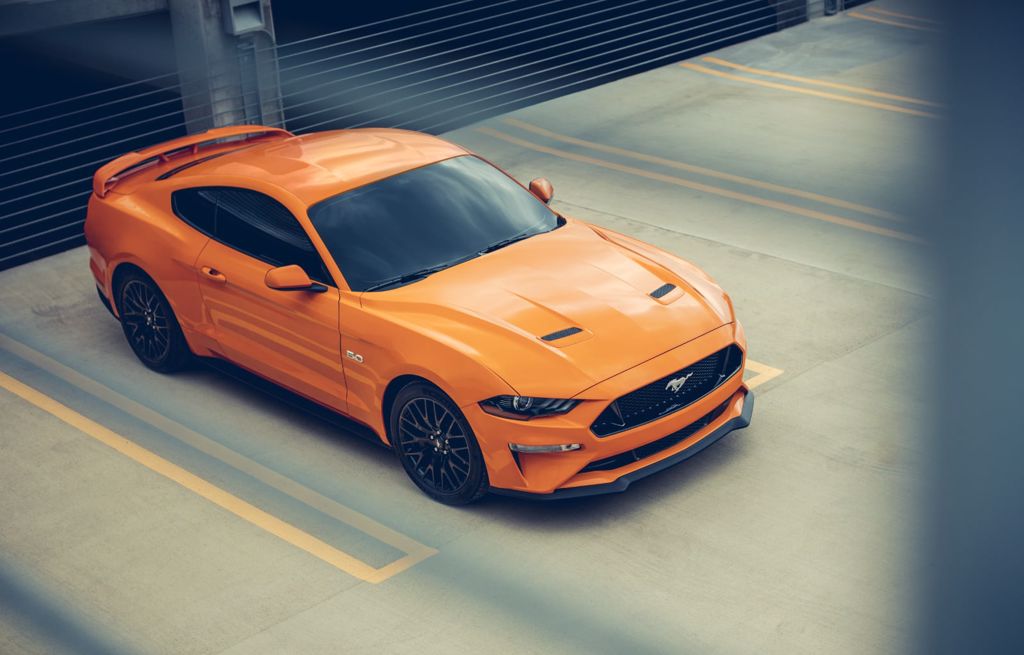
ford-jordan-mustang.jpg
live.dealer-asset.co/me1470/siteassets/ |
79 KB 79 KB |
28ms
28ms |
Image
image/jpeg |
2606:4700::6812:451 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
hqdefault.jpg
img.youtube.com/vi/J3X10c-PB8I/ Frame AA54 |
7 KB 7 KB |
172ms
110ms |
Image
image/jpeg |
2a00:1450:4001:c1f::66 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Consent
Show response
enford.cic.com.jo/ |
166 B 256 B |
96ms
96ms |
Fetch
application/json |
2606:4700::6810:1d0e Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
jquery-3.5.1.min.js
Show response
code.jquery.com/ |
87 KB 31 KB |
37ms
9ms |
Script
application/javascript |
2a04:4e42:400::411 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
dest5.html
Show response
geronimo.demdex.net/ Frame E6FE |
7 KB 3 KB |
115ms
28ms |
Document
text/html |
52.30.167.93 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
id
Show response
geronimo.d3.sc.omtrdc.net/ |
2 B 268 B |
73ms
19ms |
XHR
application/x-javascript |
63.140.62.210 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
ibs:dpid=411&dpuuid=an74gQAAABfdCgMR
dpm.demdex.net/ Redirect Chain
|
42 B 702 B |
31ms
30ms |
Image
image/gif |
52.19.120.20 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Functionality
Show response
enford.cic.com.jo/Content/Consent/Performance/ |
1 KB 493 B |
67ms
66ms |
Fetch
text/html |
2606:4700::6810:1d0e Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
js
Show response
www.googletagmanager.com/gtag/ |
455 KB 158 KB |
150ms
68ms |
Script
application/javascript |
2a00:1450:4001:c17::61 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
collect
region1.google-analytics.com/g/ |
0 0 |
54ms
19ms |
Fetch
text/plain |
2001:4860:4802:34::36 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
js
Show response
www.googletagmanager.com/gtag/ |
457 KB 158 KB |
66ms
65ms |
Script
application/javascript |
2a00:1450:4001:c17::61 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
js
Show response
www.googletagmanager.com/gtag/ |
484 KB 163 KB |
70ms
70ms |
Script
application/javascript |
2a00:1450:4001:c17::61 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
rum
Show response
enford.cic.com.jo/cdn-cgi/ |
0 174 B |
11ms
10ms |
XHR
text/plain |
2606:4700::6810:1d0e Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
favicon.ico
resources.dealer-asset.co/themes/fmlds/latest/ |
12 KB 4 KB |
20ms
20ms |
Other
image/x-icon |
2606:4700::6812:451 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
s52826178876388
geronimo.d3.sc.omtrdc.net/b/ss/geronimoprod/1/JS-2.23.0-LDQM/ |
43 B 224 B |
22ms
21ms |
Image
image/gif |
63.140.62.210 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Targeting
Show response
enford.cic.com.jo/Content/Consent/Performance/Functionality/ |
5 KB 1 KB |
92ms
91ms |
XHR
text/html |
2606:4700::6810:1d0e Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Consent
Show response
enford.cic.com.jo/ |
166 B 180 B |
57ms
57ms |
XHR
application/json |
2606:4700::6810:1d0e Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
collect
region1.google-analytics.com/g/ |
0 0 |
21ms
20ms |
Fetch
text/plain |
2001:4860:4802:34::36 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
collect
region1.google-analytics.com/g/ |
0 0 |
20ms
19ms |
Fetch
text/plain |
2001:4860:4802:34::36 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
B3403R.jpg
live.dealer-asset.co/images/me1470/banners/ |
220 KB 221 KB |
26ms
26ms |
Image
image/jpeg |
2606:4700::6812:451 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
























Verdicts & Comments Add Verdict or Comment
75 JavaScript Window variables
Go Pro
Only in urlscan Pro
Inspect and pivot on JavaScript variables, identifiers, and other key site metadata data with urlscan Pro. Reveal and search on client-side frameworks, runtime variables, and custom values.
Click for more information
Free trials of urlscan Pro are available.
These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.
object| 0 object| 1 object| 2 object| 3 object| 4 object| 5 object| fence object| GWconfig object| dataLayer function| bannerClick function| directionsClick function| contactClick function| customEventClick function| transientEventClick function| getFormEventData function| raiseFormOpenedEvent function| raiseDataLayerEvents function| raiseFormSubmitEvent function| raiseEvoEvent function| raiseSearchEvent function| raiseLegacySearchEvent function| raisePageInfoEvent function| whatsappClick function| addMutationObserver function| addEvent function| bindEventsToTarget function| addAnalyticsEvents function| smartSuppHandler function| smartsuppCheck function| chatShipperHandler function| chatShipperCheck function| Await function| Html function| Analytics object| searchEventDebounceTimer object| integrationKeys boolean| conversionSmartSupp boolean| conversionChatShipper function| whisbiOtoOpened function| phyronEventHandler function| addSmartsuppAnalytics function| chatshipperLoaded object| $czaterEvents object| clientDate string| formattedClientDate object| analyticsDatalayer object| _satellite boolean| __satelliteLoaded object| adobe function| Visitor object| s_c_il number| s_c_in function| parcelRequire5c42 object| __cfBeacon function| AppMeasurement_Module_ActivityMap function| AppMeasurement function| s_gi function| s_pgicq number| s_objectID number| s_giq object| s function| awaitJquery function| $ function| jQuery function| gtag object| google_tag_data object| google_tag_manager function| onYouTubeIframeAPIReady object| gaGlobal function| cookieWrite function| cookieRead string| g function| inList number| a object| s_i_geronimoprod10 Cookies
Go Pro
Only in urlscan Pro
Review, search, and pivot on browser cookies and persistence site data to see how a site tracks users and keeps sessions alive across visits.
Click for more information
Free trials of urlscan Pro are available.
Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.
| Domain/Path | Expires | Name / Value | |||
|---|---|---|---|---|---|
| .demdex.net/ | 1970-01-21 20:37:38 |
Name: demdex Value: 79083802867410717251866598289228212820 |
|||
| enford.cic.com.jo/ | 1969-12-31 23:59:59 |
Name: ASP.NET_SessionId Value: 3fw1i4qdtn4hfytsfrdcayb4 |
|||
| .cic.com.jo/ | 1969-12-31 23:59:59 |
Name: AMCVS_A11A079F574E92AE7F000101%40AdobeOrg Value: 1 |
|||
| .dpm.demdex.net/ | 1970-01-21 20:37:38 |
Name: dpm Value: 79083802867410717251866598289228212820 |
|||
| .cic.com.jo/ | 1970-01-22 01:54:26 |
Name: AMCV_A11A079F574E92AE7F000101%40AdobeOrg Value: 179643557%7CMCIDTS%7C20680%7CMCMID%7C78812108630177138031835471107905621426%7CMCAAMLH-1787310849%7C6%7CMCAAMB-1787310849%7CRKhpRz8krg2tLO6pguXWp5olkAcUniQYPHaMWWgdJ3xzPWQmdj0y%7CMCOPTOUT-1786713249s%7CNONE%7CMCAID%7CNONE%7CMCSYNCSOP%7C411-20687%7CvVersion%7C5.5.0 |
|||
| .cic.com.jo/ | 1970-01-22 01:54:26 |
Name: _ga Value: GA1.1.1612721595.1786706050 |
|||
| .cic.com.jo/ | 1970-01-21 16:18:27 |
Name: s_gpv Value: Welcome%20to%20%20Ford%20Jordan |
|||
| .cic.com.jo/ | 1970-01-22 01:54:26 |
Name: _ga_3YSZDM83VQ Value: GS2.1.s1786706050$o1$g0$t1786706050$j60$l0$h0 |
|||
| .cic.com.jo/ | 1970-01-22 01:54:26 |
Name: _ga_ZP6VRD4W21 Value: GS2.1.s1786706050$o1$g0$t1786706050$j60$l0$h0 |
|||
| .cic.com.jo/ | 1970-01-22 01:54:26 |
Name: _ga_F16PVKXV9Y Value: GS2.1.s1786706050$o1$g0$t1786706050$j60$l0$h0 |
Security Headers
This page lists any security headers set by the main page. If you want to understand what these mean and how to use them, head on over to this page
| Header | Value |
|---|---|
| Strict-Transport-Security | max-age=15552000; preload |
| X-Content-Type-Options | nosniff |
| X-Frame-Options | SAMEORIGIN |
| X-Xss-Protection | 1; mode=block |
Indicators
This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.
assets.adobedtm.com
cm.everesttech.net
code.jquery.com
dpm.demdex.net
enford.cic.com.jo
geronimo.d3.sc.omtrdc.net
geronimo.demdex.net
img.youtube.com
live.dealer-asset.co
region1.google-analytics.com
resources.dealer-asset.co
static.cloudflareinsights.com
www.googletagmanager.com
18.202.72.190
2001:4860:4802:34::36
2606:4700::6810:1d0e
2606:4700::6810:4f49
2606:4700::6812:451
2a00:1450:4001:c17::61
2a00:1450:4001:c1f::66
2a02:26f0:3500:587::1e80
2a04:4e42:400::411
52.19.120.20
52.30.167.93
63.140.62.210
01b68e229027a5eb26deb01df37392ffce3bf2c5c14380218f6a9f2e7211ca82
0679c14ee29c44762106c8aa4fbb0ad3d684a65a108377908796758b93c5ed18
091fc5bd2ea83ecf817258b4451cb82fcd0655698f13deb03e920bf6c060d612
0ba61c39fac511e7d8155e97ed9b3d38eee0691d136903878a526a087cf574ab
107029e9c2f48bc95bb5689c82fbacd6248a1f6b2a095930d1306c2b35e2326c
1dc3c921202b4b5ec5715bf70e054b2a5a74ed6a96cb9f00a044a4cf89d42b8f
215764183bae46263dce0194451cdbd2991757759dfb5cafd1545aed9aca4b49
220809968c035a07858ac61d24b7320200fd7fac942e6707b7d65eb976220d4f
2595496fe48df6fcf9b1bc57c29a744c121eb4dd11566466bc13d2e52e6bbcc8
2664cfd21dda1ef3a8d44a0b1e470f94449e87d8a0477fc1626c080db079737f
27c519a955289c6e33e13a0ec4bf87e8b815f3b89e6aa80d0fcd0242f4bc9311
363aee798e30425dfe3afe20d706f7ba780c3a2f78dfb66d91e42694d9102e02
378dee85e5489f787dcb545f664fd7e109330f8f20b3e913151b4984b84bcfb9
44136fa355b3678a1146ad16f7e8649e94fb4fc21fe77e8310c060f61caaff8a
47f8cdaf8e2cefb16a43efb2203b8fbc7d054f573ed705a6f65200d705767e93
4f2821bd0ba1e579948981709fc83b083a878f98ae0622e9524d26386e4447fc
5a156c840148fbc51b9b478b3c285c9f90de7e465a0906eda7192dfb72676a81
659e4dde4ba91e532c34b18b525d7e2dce020a6dcf8690a3e940ed17b7912866
672027bd68eaf3cc1484ad4e18365d3a1365a78b2d2667b74d6ef71a1ec2d2ec
6fd4b28b698ea896572f7cc3691fb11e7f9b57a70a7498f8ae6aebe96651c66b
78c1c1baf0d964522f8afab09cfc754685c1648826a7f9967fd52b774b4ec5aa
7a3f30f8c2e36b5c934f66ccaf03eef0aef2b48bddea56f12bb319d2ea26a952
7a41aff3d5601281a26576b0548c4c236424392e7ad34aeabdecf80619b6855d
7bea17a80a61ed0f54248b4ffc4c718f7c8ff2619742577a73591d62ce074da8
7f43a51028bccc7f9b2755998ed235dc84a865caba8f9f505f4c163c300e8c29
83747651520a78d13b8cbbb287aaba810ff938d9d302ae99b86677485b2fda5a
91e8d4287759439e8a4dab7eb3ad90efeb9f877e0b2051360e724c40647d062e
94e2519bf75f7bcf1bc002c88638690f959eea61f153bd69106de16000985d12
9eb4420477b86f3df78ecb3bdb71c1e23e973fe01edf88c0bbf967c560d40c5a
a1ecbaed793a1f564c49c671f2dd0ce36f858534ef6d26b55783a06b884cc506
a68f341900f143d517f3bf42bc86d98ec345eea7202e1c3c900f44b9e077a506
aa25f99d3967e7db713f6dc1b3455cd2b8698d8c67324236dad2a9e2e422686a
aec1dd89d25e119415d9fc9e2de0f9806cbc127221341fe5594573aa56e68e44
beee782ee0c5e7d64c4ef61cf7485413d04354acdf0687aab1b6040b2731181b
c6490f9656b193f497e7f4803bf578f023330d390875321661306a9c3e3a384b
c7a7143e47c315e4794d966067e6ebb81c04a3f8c9bc13f8c2073c99a374ba4c
cd53c0e9cc4ed815fa8027626e404c41c27741f09250226961533ca79f69f0b4
d6d01246a30e9d483531c27721f73f266fa4af35effdb21683ac02a620ab8aaf
d775798080bc92a87b59e8e8b631630de80e7ff780e44c4be53565c761b04809
e1ac4849b9d4a498b68f8aca01e6ed99a11d94b35a2cec533b3916b8fb722fd6
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
ee05a628decf3509aaf3b6cb539dbb8372e17590cbdae756503244865e561ad3
ee5cb3c051dac6ffcbfb0082fa7f3e912e6cf7fbb5b59edc53994b76b3597b69
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
f175336e0c163d08b4f277dd4b27bce36162d4608ef161d7cc7afb56f8c617df
f7f6a5894f1d19ddad6fa392b2ece2c5e578cbf7da4ea805b6885eb6985b6e3d