
www.panynj.gov
104.18.25.36
Public Scan
Open in
urlscan Pro
https://panynj.gov/ 9yr old
Effective URL:
https://www.panynj.gov/port-authority/en/index.html 13yr old
Submission: On August 18 via api (August 18th 2026, 5:53:15 pm UTC) from FI — Scanned from DE
Summary
TLS certificate: Issued by WE1 on June 24th 2026. Valid for: 3mo.
This is the only time www.panynj.gov was scanned on urlscan.io!
urlscan.io Verdict: No classification
Domain & IP information
| IP Address | AS Autonomous System | ||
|---|---|---|---|
| 1 1 | 104.18.24.36 104.18.24.36 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 23 | 104.18.25.36 104.18.25.36 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 167.82.49.91 167.82.49.91 | 54113 (FASTLY) (FASTLY - Fastly) | |
| 1 | 23.52.181.12 23.52.181.12 | 16625 (AKAMAI-AS) (AKAMAI-AS - Akamai Technologies) | |
| 1 | 13.226.244.71 13.226.244.71 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 2 | 192.178.183.97 192.178.183.97 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 2 | 54.217.93.58 54.217.93.58 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 1 2 | 104.18.1.22 104.18.1.22 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 176.34.106.56 176.34.106.56 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 1 1 | 54.154.173.30 54.154.173.30 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 1 | 63.140.62.120 63.140.62.120 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 1 | 13.42.137.95 13.42.137.95 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 2 | 23.194.190.163 23.194.190.163 | 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.) | |
| 3 | 157.240.253.1 157.240.253.1 | 32934 (FACEBOOK) (FACEBOOK - Facebook) | |
| 5 | 142.251.156.119 142.251.156.119 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 142.251.110.149 142.251.110.149 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 52.223.40.198 52.223.40.198 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 2 | 216.239.34.36 216.239.34.36 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 2 | 157.240.253.35 157.240.253.35 | 32934 (FACEBOOK) (FACEBOOK - Facebook) | |
| 5 | 172.64.146.215 172.64.146.215 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 142.251.20.138 142.251.20.138 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 142.251.13.95 142.251.13.95 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 172.217.117.4 172.217.117.4 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 57 | 21 |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| panynj.gov 9yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| www.panynj.gov 13yr old |
ASN16625 (AKAMAI-AS - Akamai Technologies, Inc., US)
PTR: a23-52-181-12.deploy.static.akamaitechnologies.com
| assets.adobedtm.com 13yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-13-226-244-71.fra56.r.cloudfront.net
| translations.signapsesolutions.com 2yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: lcfraw-in-f97.1e100.net
| www.googletagmanager.com 13yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: ec2-54-217-93-58.eu-west-1.compute.amazonaws.com
| dpm.demdex.net 10yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| unpkg.com 10yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: ec2-176-34-106-56.eu-west-1.compute.amazonaws.com
| panynj.demdex.net 3yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: ec2-54-154-173-30.eu-west-1.compute.amazonaws.com
| cm.everesttech.net 10yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: ip-63-140-62-120.data.adobedc.net
| panynj.tt.omtrdc.net 3yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: ec2-13-42-137-95.eu-west-2.compute.amazonaws.com
| i0lne9atrk.execute-api.eu-west-2.amazonaws.com 2yr old |
ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL)
PTR: a23-194-190-163.deploy.static.akamaitechnologies.com
| snap.licdn.com 10yr old |
ASN32934 (FACEBOOK - Facebook, Inc., US)
PTR: xx-fbcdn-shv-02-fra5.fbcdn.net
| connect.facebook.net 13yr old |
ASN15169 (GOOGLE - Google LLC, US)
| www.google.com 13yr old | |
| www.gstatic.com 10yr old | |
| fonts.gstatic.com 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: bz-in-f149.1e100.net
| ad.doubleclick.net 10yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: a6370ebea231e0c9a.awsglobalaccelerator.com
| insight.adsrvr.org 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
| region1.google-analytics.com 5yr old |
ASN32934 (FACEBOOK - Facebook, Inc., US)
PTR: edge-star-mini-shv-02-fra5.facebook.com
| www.facebook.com 11yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| px.ads.linkedin.com 9yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: bx-in-f138.1e100.net
| translate.google.com 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: wt-in-f95.1e100.net
| translate.googleapis.com 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
| translate-pa.googleapis.com 5yr old |
| Apex Domain Subdomains |
Transfer | |
|---|---|---|
| 24 |
panynj.gov
2 redirects
panynj.gov — Cisco Umbrella Rank: 523673 9yr old www.panynj.gov 13yr old |
5 MB |
| 5 |
linkedin.com
px.ads.linkedin.com — Cisco Umbrella Rank: 600 9yr old |
4 KB |
| 4 |
gstatic.com
www.gstatic.com — Cisco Umbrella Rank: 10 10yr old fonts.gstatic.com — Cisco Umbrella Rank: 64 10yr old |
10 KB |
| 3 |
facebook.net
connect.facebook.net — Cisco Umbrella Rank: 247 13yr old |
194 KB |
| 3 |
demdex.net
dpm.demdex.net — Cisco Umbrella Rank: 519 10yr old panynj.demdex.net 3yr old |
5 KB |
| 2 |
googleapis.com
translate.googleapis.com — Cisco Umbrella Rank: 1015 10yr old translate-pa.googleapis.com — Cisco Umbrella Rank: 1751 5yr old |
95 KB |
| 2 |
facebook.com
www.facebook.com — Cisco Umbrella Rank: 123 11yr old |
35 B |
| 2 |
google-analytics.com
region1.google-analytics.com — Cisco Umbrella Rank: 4404 5yr old |
|
| 2 |
google.com
www.google.com — Cisco Umbrella Rank: 6 13yr old translate.google.com — Cisco Umbrella Rank: 1804 10yr old |
1 KB |
| 2 |
licdn.com
snap.licdn.com — Cisco Umbrella Rank: 1658 10yr old |
39 KB |
| 2 |
unpkg.com
1 redirects
unpkg.com — Cisco Umbrella Rank: 1006 10yr old |
3 KB |
| 2 |
googletagmanager.com
www.googletagmanager.com — Cisco Umbrella Rank: 82 13yr old |
342 KB |
| 1 |
adsrvr.org
insight.adsrvr.org — Cisco Umbrella Rank: 1716 10yr old |
149 B |
| 1 |
doubleclick.net
ad.doubleclick.net — Cisco Umbrella Rank: 189 10yr old |
|
| 1 |
amazonaws.com
i0lne9atrk.execute-api.eu-west-2.amazonaws.com 2yr old |
1 KB |
| 1 |
omtrdc.net
panynj.tt.omtrdc.net 3yr old |
843 B |
| 1 |
everesttech.net
1 redirects
cm.everesttech.net — Cisco Umbrella Rank: 2913 10yr old |
490 B |
| 1 |
signapsesolutions.com
translations.signapsesolutions.com 2yr old |
99 KB |
| 1 |
adobedtm.com
assets.adobedtm.com — Cisco Umbrella Rank: 417 13yr old |
64 KB |
| 1 |
hlx.page
rum.hlx.page — Cisco Umbrella Rank: 7289 4yr old |
3 KB |
| 57 | 20 |
| Domain | Requested by | |
|---|---|---|
| 23 | www.panynj.gov |
1 redirects
www.panynj.gov
|
| 5 | px.ads.linkedin.com |
snap.licdn.com
www.panynj.gov |
| 3 | www.gstatic.com |
translate.google.com
www.gstatic.com |
| 3 | connect.facebook.net |
www.panynj.gov
connect.facebook.net |
| 2 | www.facebook.com |
www.panynj.gov
|
| 2 | region1.google-analytics.com |
www.googletagmanager.com
|
| 2 | snap.licdn.com |
www.googletagmanager.com
snap.licdn.com |
| 2 | unpkg.com |
1 redirects
www.panynj.gov
|
| 2 | dpm.demdex.net |
assets.adobedtm.com
www.panynj.gov |
| 2 | www.googletagmanager.com |
www.panynj.gov
www.googletagmanager.com |
| 1 | translate-pa.googleapis.com | |
| 1 | fonts.gstatic.com | |
| 1 | translate.googleapis.com |
translate.google.com
|
| 1 | translate.google.com |
www.panynj.gov
|
| 1 | insight.adsrvr.org |
www.panynj.gov
|
| 1 | ad.doubleclick.net |
www.googletagmanager.com
|
| 1 | www.google.com |
www.googletagmanager.com
|
| 1 | i0lne9atrk.execute-api.eu-west-2.amazonaws.com |
translations.signapsesolutions.com
|
| 1 | panynj.tt.omtrdc.net |
assets.adobedtm.com
|
| 1 | cm.everesttech.net | 1 redirects |
| 1 | panynj.demdex.net |
assets.adobedtm.com
|
| 1 | translations.signapsesolutions.com |
www.panynj.gov
|
| 1 | assets.adobedtm.com |
www.panynj.gov
|
| 1 | rum.hlx.page |
www.panynj.gov
|
| 1 | panynj.gov | 1 redirects |
| 57 | 25 |
This site contains links to these domains. Also see Links.
| Domain |
|---|
| www.jointheportauthority.com |
| new.mta.info |
| www.njtransit.com |
| www.portauthoritybuilds.com |
| portauthoritybuilds.com |
| twitter.com |
| translate.google.com |
| Subject Issuer | Validity | Valid | |
|---|---|---|---|
| www.panynj.gov WE1 |
2026-06-24 - 2026-09-22 |
3mo | crt.sh |
| hlx.page YR2 |
2026-07-27 - 2026-10-25 |
3mo | crt.sh |
| assets.adobedtm.com DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2026-06-15 - 2026-12-30 |
7mo | crt.sh |
| *.signapsesolutions.com Amazon RSA 2048 M01 |
2026-07-20 - 2027-02-02 |
7mo | crt.sh |
| *.google-analytics.com WE2 |
2026-08-05 - 2026-10-28 |
3mo | crt.sh |
| *.demdex.com DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2025-10-14 - 2026-11-14 |
1yr | crt.sh |
| *.tt.omtrdc.net DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2026-02-17 - 2027-03-20 |
1yr | crt.sh |
| *.execute-api.eu-west-2.amazonaws.com Amazon RSA 2048 M01 |
2026-07-19 - 2027-02-01 |
7mo | crt.sh |
| *.licdn.com DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2025-10-14 - 2026-10-13 |
1yr | crt.sh |
| *.facebook.com DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2026-05-28 - 2026-08-26 |
3mo | crt.sh |
| *.google.com WE2 |
2026-08-05 - 2026-10-28 |
3mo | crt.sh |
| *.doubleclick.net WE2 |
2026-08-05 - 2026-10-28 |
3mo | crt.sh |
| *.adsrvr.org GlobalSign GCC R3 DV TLS CA 2020 |
2026-03-04 - 2027-04-02 |
1yr | crt.sh |
| www.linkedin.com DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2026-03-19 - 2026-09-19 |
6mo | crt.sh |
| upload.video.google.com WE2 |
2026-08-05 - 2026-10-28 |
3mo | crt.sh |
This page contains 3 frames:
Primary Page:
https://www.panynj.gov/port-authority/en/index.html
Frame ID: 4CB6CB4B3D52004946CC53FC96BA5C35
Requests: 55 HTTP requests in this frame
Frame:
https://panynj.demdex.net/dest5.html?d_nsid=0
Frame ID: 8EE1AA0045F498A3B3193307599DFAA7
Requests: 1 HTTP requests in this frame
Frame:
https://translate-pa.googleapis.com/v1/supportedLanguages?client=te&display_language=de&key=AIzaSyBWDj0QJvVIx8XOhRegXX5_SrRWxhT5Hs4&callback=callback
Frame ID: AFCE8F18E3B2AF33286AD018CA572E8A
Requests: 1 HTTP requests in this frame
Screenshot
Page Title
We Keep the Region Moving | Port Authority of New York and New JerseyPage URL History Show full URLs
-
https://panynj.gov/
HTTP 301
https://www.panynj.gov/ HTTP 301
https://www.panynj.gov/port-authority/en/index.html Page URL
Detected technologies
 Adobe Experience Manager
(CMS)
Expand
Detected patterns
- <div class="[^"]*aem-Grid
- /etc\.clientlibs/
 Adobe Audience Manager
(Segmentation)
Expand
Detected patterns
 Cloudflare Bot Management
(Security)
Expand
Detected patterns
 DoubleClick Floodlight
(Advertising)
Expand
Detected patterns
- \.doubleclick\.net
 Facebook Pixel
(Analytics)
Expand
Detected patterns
- connect\.facebook\.\w+/.+/fbevents\.js
- connect\.facebook.\w+/signals/config/\d+\?v=([\d\.]+)
 Google Analytics
(Analytics)
Expand
Detected patterns
- googletagmanager\.com/gtag/js
 Google Tag Manager
(Tag managers)
Expand
Detected patterns
- googletagmanager\.com/ns\.html[^>]+></iframe>
- googletagmanager\.com/gtm\.js
- \.googletagmanager\.com/
 Linkedin Insight Tag
(Analytics)
Expand
Detected patterns
- snap\.licdn\.com/li\.lms-analytics/insight\.min\.js
 theTradeDesk
(Advertising)
Expand
Detected patterns
- \.adsrvr\.org/
 Unpkg
(CDN)
Expand
Detected patterns
- unpkg\.com/
Page Statistics
13 Outgoing links
These are links going to different origins than the main page.
Title: Careers
Search URL Search Domain Scan URL
Title: New York City MTA
Search URL Search Domain Scan URL
Title: New Jersey Transit
Search URL Search Domain Scan URL
Title: Learn More
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Title: Midtown Bus Terminal Replacement
Search URL Search Domain Scan URL
Title: Follow @PANYNJ on Twitter
Search URL Search Domain Scan URL
Title: Follow @JFKairport on Twitter
Search URL Search Domain Scan URL
Title: Follow @SWFairport on Twitter
Search URL Search Domain Scan URL
Title: Follow @LGAairport on Twitter
Search URL Search Domain Scan URL
Title: Follow @EWRairport on Twitter
Search URL Search Domain Scan URL
Title: Follow @PATHTrain on Twitter
Search URL Search Domain Scan URL
Title: Google Übersetzer
Search URL Search Domain Scan URL
Page URL History
This captures the URL locations of the websites, including HTTP redirects and client-side redirects via JavaScript or Meta fields.
-
https://panynj.gov/
HTTP 301
https://www.panynj.gov/ HTTP 301
https://www.panynj.gov/port-authority/en/index.html Page URL
Redirected requests
There were HTTP redirect chains for the following requests:
Request Chain 7- https://unpkg.com/@webcomponents/webcomponentsjs@%5E2/webcomponents-loader.js HTTP 302
- https://unpkg.com/@webcomponents/webcomponentsjs@2.8.0/webcomponents-loader.js
- https://cm.everesttech.net/cm/dd?d_uuid=37547500661523262480107864203794139829 HTTP 302
- https://dpm.demdex.net/ibs:dpid=411&dpuuid=aoScDAAAADmsSg-z
57 HTTP transactions
0 data transactions
| Method Protocol |
Status | Resource Path |
Size x-fer |
Time Latency |
Type MIME-Type |
IP Location |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
|
GET H2 |
200 |
Primary Request
index.html
Show response
www.panynj.gov/port-authority/en/ Redirect Chain
|
3 KB 1 KB |
155ms
155ms |
Document
text/html |
104.18.25.36 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
rum-standalone.js
Show response
rum.hlx.page/.rum/@adobe/helix-rum-js@%5E2/dist/ |
7 KB 3 KB |
112ms
45ms |
Script
text/javascript |
167.82.49.91 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
portauthority-react.min.c51ca0709d8e944376f23e5313c0b186.css
www.panynj.gov/etc.clientlibs/portauthority/clientlibs/ |
801 KB 90 KB |
63ms
62ms |
Stylesheet
text/css |
104.18.25.36 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
launch-e05b0865ec40.min.js
Show response
assets.adobedtm.com/c6adea92c19a/404d67103111/ |
197 KB 64 KB |
153ms
47ms |
Script
application/x-javascript |
23.52.181.12 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
portauthority-react.min.js
Show response
www.panynj.gov/etc.clientlibs/portauthority/clientlibs/ |
4 MB 1 MB |
116ms
115ms |
Script
application/javascript |
104.18.25.36 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
/
Show response
translations.signapsesolutions.com/ |
283 KB 99 KB |
249ms
105ms |
Script
application/javascript |
13.226.244.71 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
gtm.js
Show response
www.googletagmanager.com/ |
544 KB 176 KB |
187ms
74ms |
Script
application/javascript |
192.178.183.97 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
id
Show response
dpm.demdex.net/ |
365 B 916 B |
203ms
76ms |
XHR
application/json |
54.217.93.58 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
webcomponents-loader.js
Show response
unpkg.com/@webcomponents/webcomponentsjs@2.8.0/ Redirect Chain
|
8 KB 3 KB |
38ms
37ms |
Script
text/javascript |
104.18.1.22 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
dest5.html
Show response
panynj.demdex.net/ Frame 8EE1 |
7 KB 3 KB |
217ms
66ms |
Document
text/html |
176.34.106.56 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
ibs:dpid=411&dpuuid=aoScDAAAADmsSg-z
dpm.demdex.net/ Redirect Chain
|
42 B 704 B |
49ms
49ms |
Image
image/gif |
54.217.93.58 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
delivery
Show response
panynj.tt.omtrdc.net/rest/v1/ |
349 B 843 B |
246ms
120ms |
XHR
application/json |
63.140.62.120 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
en.model.json
Show response
www.panynj.gov/content/port-authority/ |
6 MB 815 KB |
258ms
258ms |
Fetch
application/json |
104.18.25.36 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
4f0e1a3c-dc1a-4520-8bec-549a50210202
Show response
i0lne9atrk.execute-api.eu-west-2.amazonaws.com/prod/v1/web-translation/config/ |
1 KB 1 KB |
226ms
115ms |
Fetch
application/json |
13.42.137.95 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
js
Show response
www.googletagmanager.com/gtag/ |
486 KB 166 KB |
66ms
66ms |
Script
application/javascript |
192.178.183.97 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
insight.min.js
Show response
snap.licdn.com/li.lms-analytics/ |
56 KB 20 KB |
148ms
52ms |
Script
application/javascript |
23.194.190.163 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
fbevents.js
Show response
connect.facebook.net/en_US/ |
400 KB 105 KB |
59ms
29ms |
Script
application/x-javascript |
157.240.253.1 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
200 |
collect
www.google.com/ccm/ |
0 0 |
83ms
42ms |
Fetch
text/plain |
142.251.156.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
204 |
collect
ad.doubleclick.net/ccm/s/ |
0 0 |
85ms
42ms |
Fetch
text/html |
142.251.110.149 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
/
insight.adsrvr.org/track/pxl/ |
70 B 149 B |
539ms
278ms |
Image
image/gif |
52.223.40.198 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
1716708712033173
Show response
connect.facebook.net/signals/config/ |
285 KB 67 KB |
104ms
104ms |
Script
application/x-javascript |
157.240.253.1 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
collect
region1.google-analytics.com/g/ |
0 0 |
112ms
47ms |
Fetch
text/plain |
216.239.34.36 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
insight.old.min.js
Show response
snap.licdn.com/li.lms-analytics/ |
52 KB 19 KB |
45ms
45ms |
Script
application/javascript |
23.194.190.163 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
984166902935835
Show response
connect.facebook.net/signals/config/ |
125 KB 22 KB |
95ms
94ms |
Script
application/x-javascript |
157.240.253.1 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
/
www.facebook.com/tr/ |
0 19 B |
58ms
28ms |
Image
text/plain |
157.240.253.35 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
/
px.ads.linkedin.com/wa/ |
0 0 |
307ms
252ms |
Fetch
|
172.64.146.215 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
attribution_trigger
Show response
px.ads.linkedin.com/ |
2 B 1022 B |
333ms
281ms |
XHR
application/json |
172.64.146.215 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
collect
px.ads.linkedin.com/ |
0 917 B |
243ms
191ms |
Image
application/javascript |
172.64.146.215 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
attribution_trigger
Show response
px.ads.linkedin.com/ |
2 B 1 KB |
242ms
190ms |
XHR
application/json |
172.64.146.215 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
collect
px.ads.linkedin.com/ |
0 727 B |
268ms
217ms |
Image
application/javascript |
172.64.146.215 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
/
www.facebook.com/tr/ |
0 16 B |
28ms
28ms |
Image
text/plain |
157.240.253.35 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
icons.99596eb7.svg
www.panynj.gov/etc.clientlibs/portauthority/clientlibs/portauthority-react/resources/static/media/ |
77 KB 29 KB |
57ms
56ms |
Other
image/svg+xml |
104.18.25.36 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
image.jpg
www.panynj.gov/content/dam/port-authority/home/01%20-%20TOC%20-%20Key%20Background%20Image.jpg.transform/transform-1920/ |
414 KB 414 KB |
74ms
74ms |
Image
image/jpeg |
104.18.25.36 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
image.jpg
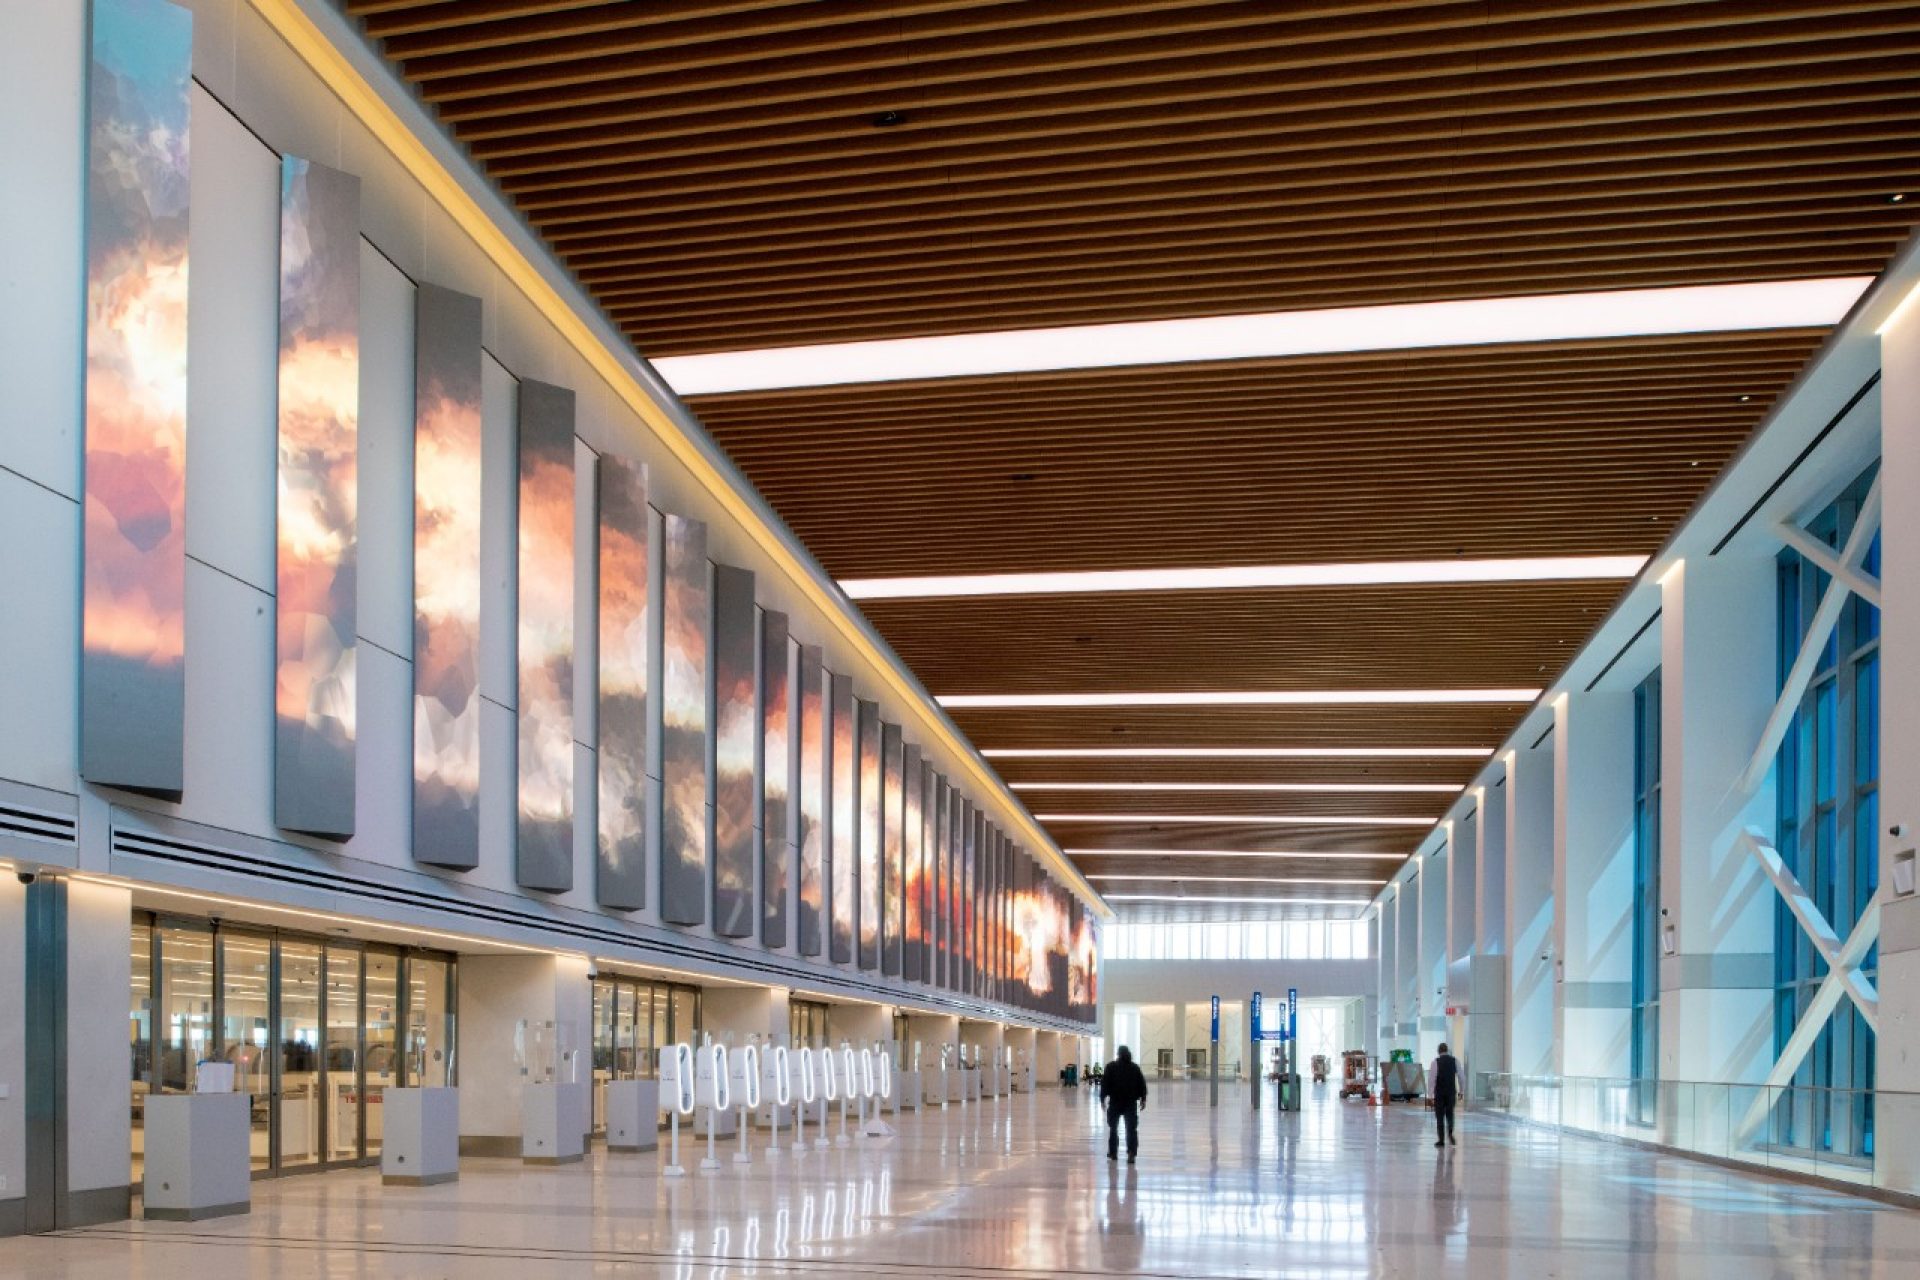
www.panynj.gov/content/dam/airports/index/ewr-terminal-a/ewr-nta-7.PNG.transform/transform-1920/ |
576 KB 577 KB |
76ms
76ms |
Image
image/jpeg |
104.18.25.36 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
GTAmerica-RegularItalic.ttf
www.panynj.gov/etc.clientlibs/portauthority/clientlibs/portauthority-react/resources/fonts/ |
108 KB 51 KB |
60ms
59ms |
Font
application/x-font-ttf |
104.18.25.36 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
GTAmerica-Bold.ttf
www.panynj.gov/etc.clientlibs/portauthority/clientlibs/portauthority-react/resources/fonts/ |
102 KB 50 KB |
58ms
57ms |
Font
application/x-font-ttf |
104.18.25.36 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
GTAmerica-ExtendedBold.ttf
www.panynj.gov/etc.clientlibs/portauthority/clientlibs/portauthority-react/resources/fonts/ |
105 KB 51 KB |
58ms
57ms |
Font
application/x-font-ttf |
104.18.25.36 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
GTAmerica-Regular.ttf
www.panynj.gov/etc.clientlibs/portauthority/clientlibs/portauthority-react/resources/fonts/ |
101 KB 48 KB |
57ms
55ms |
Font
application/x-font-ttf |
104.18.25.36 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
GTAmerica-ExtendedBlack.ttf
www.panynj.gov/etc.clientlibs/portauthority/clientlibs/portauthority-react/resources/fonts/ |
104 KB 50 KB |
64ms
63ms |
Font
application/x-font-ttf |
104.18.25.36 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
GTAmerica-Black.ttf
www.panynj.gov/etc.clientlibs/portauthority/clientlibs/portauthority-react/resources/fonts/ |
101 KB 48 KB |
80ms
79ms |
Font
application/x-font-ttf |
104.18.25.36 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
element.js
Show response
translate.google.com/translate_a/ |
3 KB 1 KB |
159ms
62ms |
Script
text/javascript |
142.251.20.138 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Wordmark.svg
www.panynj.gov/content/dam/path/global/ |
7 KB 3 KB |
77ms
75ms |
Image
image/svg+xml |
104.18.25.36 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Port_Authority_footer%20logo.png
www.panynj.gov/content/dam/police/global/ |
89 KB 89 KB |
97ms
94ms |
Image
image/png |
104.18.25.36 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
image.jpg
www.panynj.gov/content/dam/port-authority/home/13_PABTR_9th-Ave-PANYNJ.png.transform/transform-1920/ |
586 KB 587 KB |
85ms
83ms |
Image
image/jpeg |
104.18.25.36 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
image.jpg
www.panynj.gov/content/dam/port-authority/press-room/lga%20terminal%20C.jpg.transform/transform-1920/ |
381 KB 382 KB |
84ms
82ms |
Image
image/jpeg |
104.18.25.36 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
image.jpg
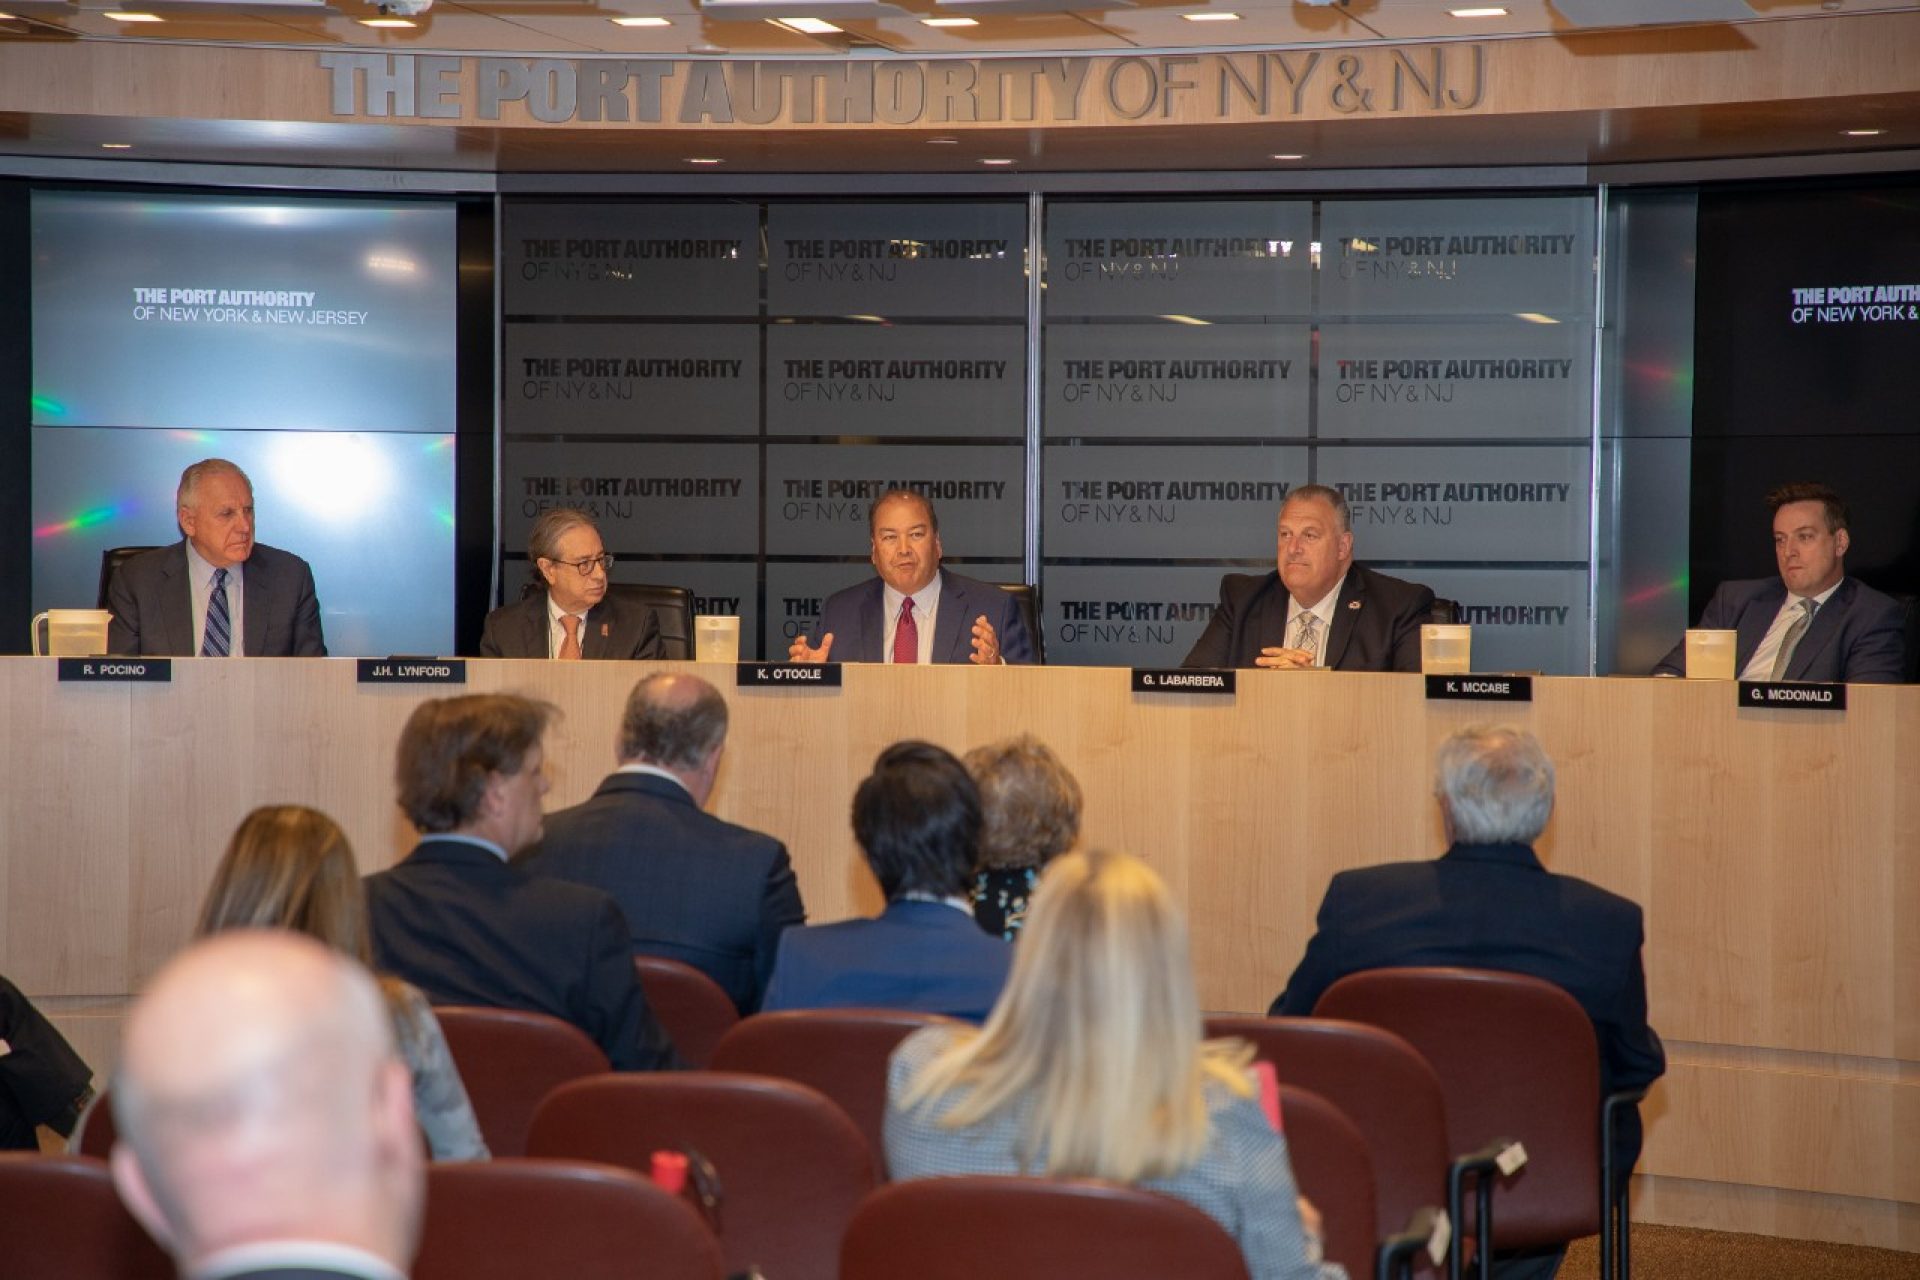
www.panynj.gov/content/dam/airports/index/20190523%20Board%20Meeting%200013.jpg.transform/transform-1920/ |
248 KB 248 KB |
78ms
76ms |
Image
image/jpeg |
104.18.25.36 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
image.jpg
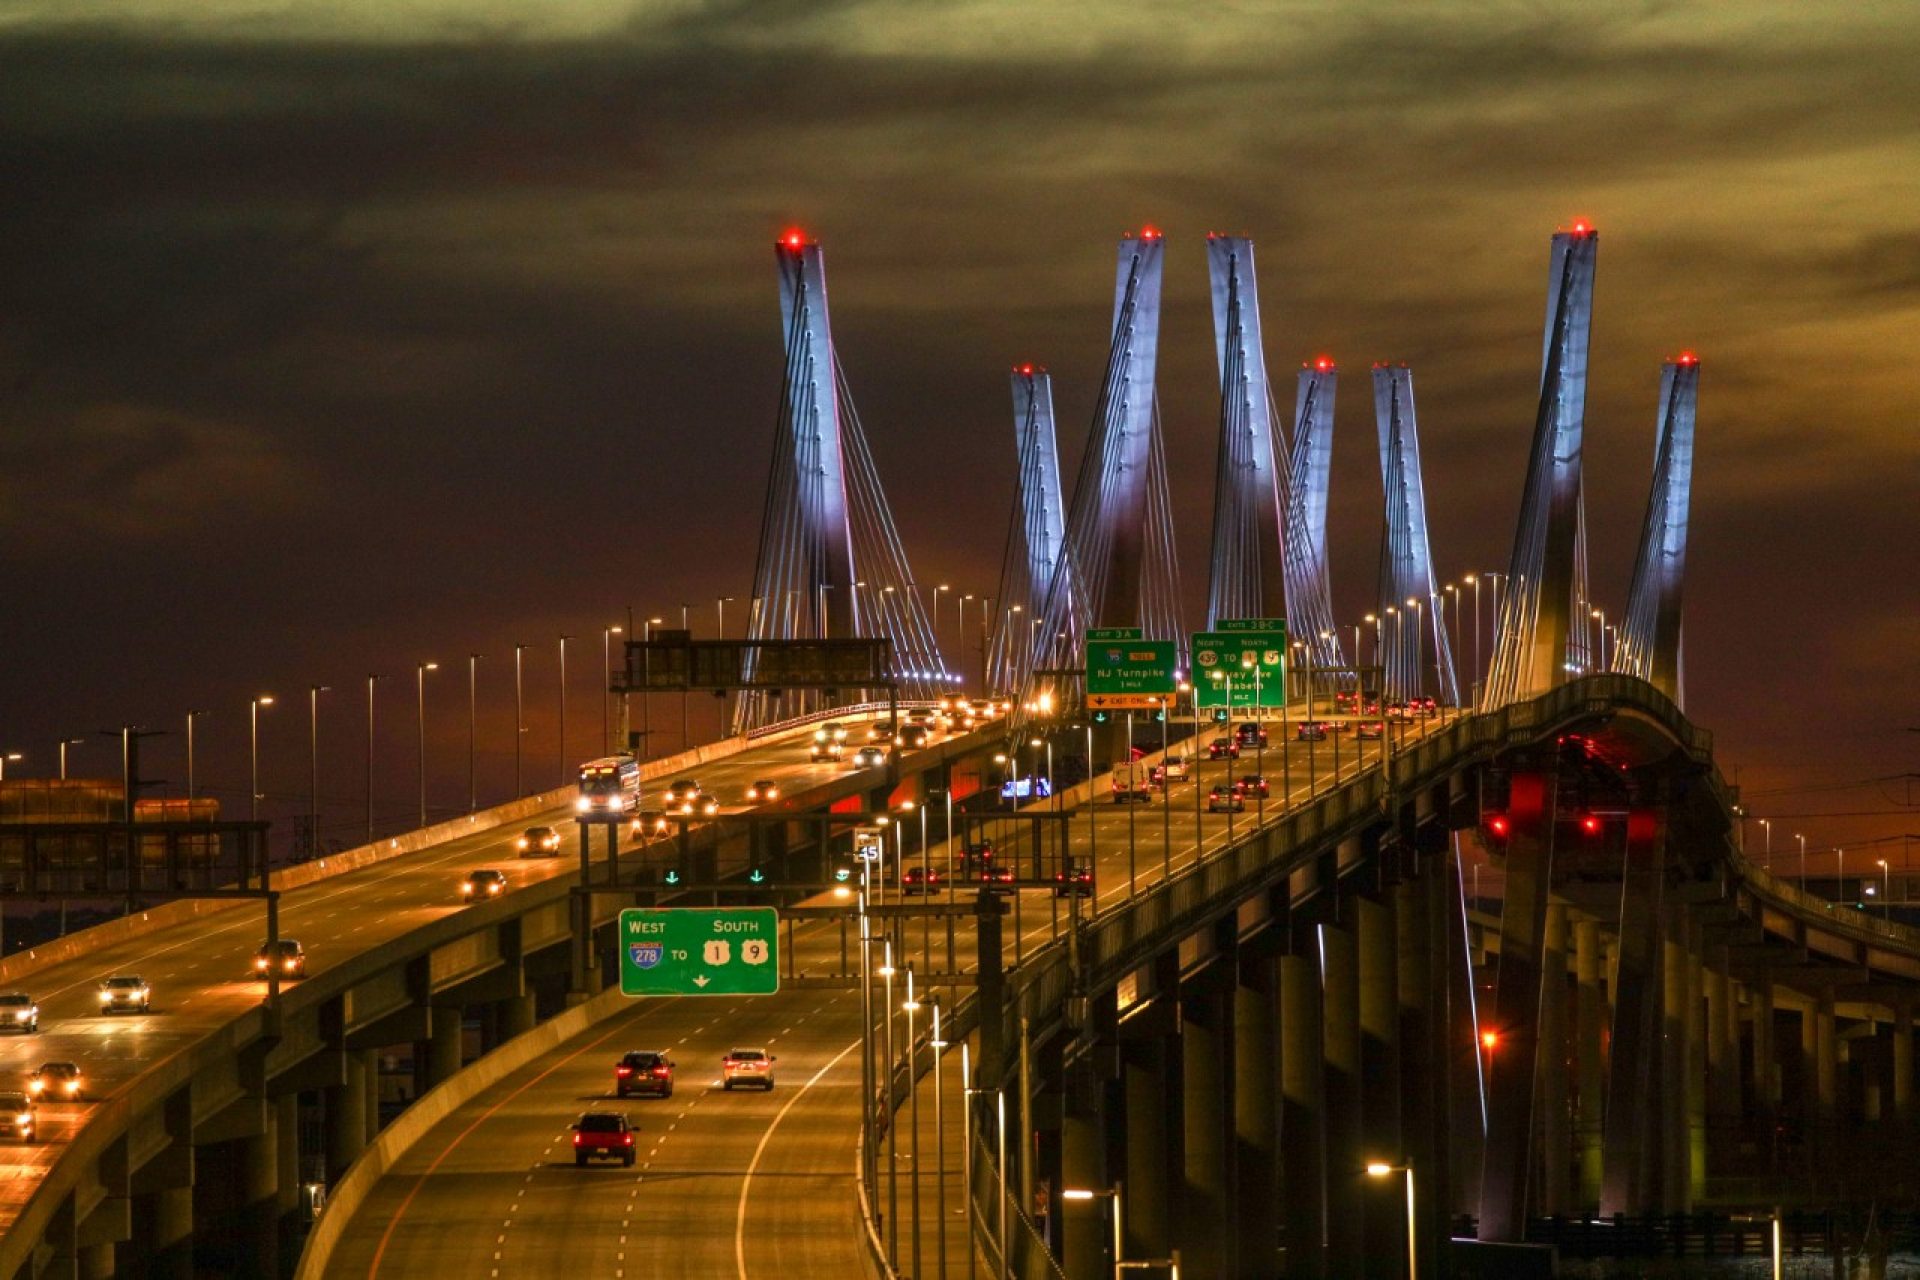
www.panynj.gov/content/dam/airports/index/20190424%20Goethals%20Bridge%20Dusk%20113.jpg.transform/transform-1920/ |
301 KB 302 KB |
89ms
88ms |
Image
image/jpeg |
104.18.25.36 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
image.jpg
www.panynj.gov/content/dam/port-authority/global/shutterstock_719438779.jpg.transform/transform-1920/ |
166 KB 166 KB |
94ms
92ms |
Image
image/jpeg |
104.18.25.36 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
icons.99596eb7.svg
Show response
www.panynj.gov/etc.clientlibs/portauthority/clientlibs/portauthority-react/resources/static/media/ |
77 KB 0 |
1ms
1ms |
XHR
image/svg+xml |
104.18.25.36 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
404 |
favicon.ico
www.panynj.gov/ |
677 B 910 B |
71ms
70ms |
Other
text/html |
104.18.25.36 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
m=el_main_css
www.gstatic.com/_/translate_http/_/ss/k=translate_http.tr.zZZZhVqDDCw.L.W.O/am=BESFAw/d=0/rs=AN8SPforq2_8TtnxsZbpPQABz4vfaNFrbQ/ |
22 KB 4 KB |
36ms
35ms |
Stylesheet
text/css |
142.251.156.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
m=el_main
Show response
translate.googleapis.com/_/translate_http/_/js/k=translate_http.tr.de._oN3CULm23M.O/am=BESFAw/d=1/ed=1/rs=AN8SPfpsLkHx4QRJh74lnXNN22Qz1QQQkA/ |
261 KB 92 KB |
107ms
38ms |
Script
text/javascript |
142.251.13.95 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
24px.svg
fonts.gstatic.com/s/i/productlogos/translate/v14/ |
6 KB 3 KB |
36ms
35ms |
Image
image/svg+xml |
142.251.156.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
googlelogo_color_42x16dp.png
www.gstatic.com/images/branding/googlelogo/1x/ |
910 B 934 B |
67ms
67ms |
Image
image/png |
142.251.156.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
translate_24dp.png
www.gstatic.com/images/branding/product/2x/ |
2 KB 2 KB |
95ms
95ms |
Image
image/png |
142.251.156.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
supportedLanguages
Show response
translate-pa.googleapis.com/v1/ Frame AFCE |
31 KB 3 KB |
158ms
77ms |
Script
text/javascript |
172.217.117.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
collect
region1.google-analytics.com/g/ |
0 0 |
39ms
39ms |
Fetch
text/plain |
216.239.34.36 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||












Verdicts & Comments Add Verdict or Comment
59 JavaScript Window variables
These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.
object| 0 object| 1 object| dataLayer object| _satellite boolean| __satelliteLoaded object| adobe function| Visitor object| s_c_il number| s_c_in object| __target_telemetry object| ___target_traces function| mboxCreate function| mboxDefine function| mboxUpdate object| webpackJsonpreact-app object| __core-js_shared__ object| core function| setImmediate function| clearImmediate object| regeneratorRuntime object| cptable object| gsapVersions function| _ object| options object| _sentryDebugIds string| _sentryDebugIdIdentifier function| reactiveElementPolyfillSupport function| litHtmlPolyfillSupport function| litElementPolyfillSupport object| SENTRY_RELEASE object| litPropertyMetadata object| reactiveElementVersions object| litHtmlVersions object| litElementVersions string| RUM_BASE object| RUM_PARAMS object| hlx object| google_tag_manager function| postscribe object| google_tag_manager_external object| __SENTRY__ object| google_tag_data object| _linkedin_data_partner_ids boolean| _already_called_lintrk function| fbq function| _fbq object| WebComponents function| onYouTubeIframeAPIReady object| gaGlobal function| lintrk object| ORIBILI object| picturefillCFG function| picturefill function| _DumpException object| google function| googleTranslateElementInit object| default_tr object| _F_toggles_default_tr object| closure_lm_74697119 Cookies
Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.
| Domain/Path | Expires | Name / Value | |||
|---|---|---|---|---|---|
| panynj.gov/ | 1969-12-31 23:59:59 |
Name: ApplicationGatewayAffinityCORS Value: 82344efa8b2a852143a5d382aeebc846 |
|||
| panynj.gov/ | 1969-12-31 23:59:59 |
Name: ApplicationGatewayAffinity Value: 82344efa8b2a852143a5d382aeebc846 |
|||
| .panynj.gov/ | 1970-01-21 16:24:37 |
Name: __cf_bm Value: CIaspBct7lxxrJSKGmaJMqsdy0md8Ogqwh.p.4_1qY0-1787075595.5651617-1.0.1.1-X__ANI8jYMmX_7yQhkVOsHLpRVIWCUB7yhRPtELMAM.OEWiidUvKNdzKDLnkRuUZN6wtnPTAHRVQHH9.msHclATH1A5JxDH7RwQPUZ617a7Wt0Ox5425HQ5g2fhEAE0l |
|||
| www.panynj.gov/ | 1969-12-31 23:59:59 |
Name: ApplicationGatewayAffinityCORS Value: 82344efa8b2a852143a5d382aeebc846 |
|||
| www.panynj.gov/ | 1969-12-31 23:59:59 |
Name: ApplicationGatewayAffinity Value: 82344efa8b2a852143a5d382aeebc846 |
|||
| .panynj.gov/ | 1969-12-31 23:59:59 |
Name: at_check Value: true |
|||
| .demdex.net/ | 1970-01-21 20:43:47 |
Name: demdex Value: 37547500661523262480107864203794139829 |
|||
| .panynj.gov/ | 1969-12-31 23:59:59 |
Name: AMCVS_128A34A45CEBB0530A495C36%40AdobeOrg Value: 1 |
|||
| .panynj.gov/ | 1970-01-21 18:34:11 |
Name: _gcl_au Value: 1.1.895763748.1787075597 |
|||
| .dpm.demdex.net/ | 1970-01-21 20:43:47 |
Name: dpm Value: 37547500661523262480107864203794139829 |
|||
| .panynj.gov/ | 1970-01-22 02:00:35 |
Name: _ga Value: GA1.1.562605851.1787075597 |
|||
| .panynj.gov/ | 1970-01-22 02:00:35 |
Name: _ga_GTNH9SBV9T Value: GS2.1.s1787075597$o1$g0$t1787075597$j60$l0$h0 |
|||
| .panynj.gov/ | 1970-01-22 02:00:35 |
Name: mbox Value: session#9705cdaf3156411cb8a38648bd0fd825#1787077458|PC#9705cdaf3156411cb8a38648bd0fd825.37_0#1850320398 |
|||
| .panynj.gov/ | 1970-01-22 02:00:35 |
Name: AMCV_128A34A45CEBB0530A495C36%40AdobeOrg Value: 179643557%7CMCIDTS%7C20684%7CMCMID%7C43623656141391464690715655387967622712%7CMCAAMLH-1787680396%7C6%7CMCAAMB-1787680396%7C6G1ynYcLPuiQxYZrsz_pkqfLG9yMXBpb2zX5dvJdYQJzPXImdj0y%7CMCOPTOUT-1787082796s%7CNONE%7CMCSYNCSOP%7C411-20691%7CvVersion%7C5.5.0 |
|||
| .panynj.gov/ | 1970-01-21 18:34:11 |
Name: _fbp Value: fb.1.1787075597211.805371633420361774 |
|||
| .linkedin.com/ | 1970-01-22 01:10:11 |
Name: bcookie Value: "v=2&291cddc3-889d-472c-8055-54286b77a6c7" |
|||
| .linkedin.com/ | 1970-01-21 20:43:47 |
Name: li_gc Value: MTswOzE3ODcwNzU1OTc7MjswMjF3jGUIiaaCm+zoYdYMWrctN3JNZ4/C0+T/cOPqb/retQ== |
|||
| .linkedin.com/ | 1970-01-21 16:26:01 |
Name: lidc Value: "b=OGST06:s=O:r=O:a=O:p=O:g=3585:u=1:x=1:i=1787075597:t=1787161997:v=2:sig=AQGkcF-EdSpCMzpn9IRfSsOQ1PukL1rk" |
|||
| .linkedin.com/ | 1970-01-21 16:24:37 |
Name: __cf_bm Value: NvY3hLSsxcL2UeohPHPcZnISclkGYk31leH0mB58MbQ-1787075597.2893734-1.0.1.1-Mt16MM6jdYj0_VDwQu2zZc4BANlhNRF4dEyrA83S.tmjMSPjv6UVU1tMR8TvwIAvmK1OAX3CF9Ib.mzQB1TnyOefVRYUiFjPtYL5p6iV9rXyR5sDdGlgw4l0GIiUn3yc |
2 Console Messages
A page may trigger messages to the console to be logged. These are often error messages about being unable to load a resource or execute a piece of JavaScript. Sometimes they also provide insight into the technology behind a website.
| Source | Level | URL Text |
|---|
Security Headers
This page lists any security headers set by the main page. If you want to understand what these mean and how to use them, head on over to this page
| Header | Value |
|---|---|
| Content-Security-Policy | default-src 'self' https: data: blob: 'unsafe-inline' 'unsafe-eval'; base-uri 'self'; object-src 'none'; frame-ancestors 'self'; |
| Strict-Transport-Security | max-age=31536000; includeSubDomains; preload |
| X-Content-Type-Options | nosniff |
| X-Frame-Options | SAMEORIGIN |
Indicators
This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.
ad.doubleclick.net
assets.adobedtm.com
cm.everesttech.net
connect.facebook.net
dpm.demdex.net
fonts.gstatic.com
i0lne9atrk.execute-api.eu-west-2.amazonaws.com
insight.adsrvr.org
panynj.demdex.net
panynj.gov
panynj.tt.omtrdc.net
px.ads.linkedin.com
region1.google-analytics.com
rum.hlx.page
snap.licdn.com
translate-pa.googleapis.com
translate.google.com
translate.googleapis.com
translations.signapsesolutions.com
unpkg.com
www.facebook.com
www.google.com
www.googletagmanager.com
www.gstatic.com
www.panynj.gov
104.18.1.22
104.18.24.36
104.18.25.36
13.226.244.71
13.42.137.95
142.251.110.149
142.251.13.95
142.251.156.119
142.251.20.138
157.240.253.1
157.240.253.35
167.82.49.91
172.217.117.4
172.64.146.215
176.34.106.56
192.178.183.97
216.239.34.36
23.194.190.163
23.52.181.12
52.223.40.198
54.154.173.30
54.217.93.58
63.140.62.120
055dda98dbe8ae04ce1fe514af9139363f2b75a591ea0e6e49c85798c6bc13af
0a4564e34f1e2597d666c08a2cc430ef6dd74c23030c93fbc59faab77fcfa194
0ecbd1374ebd05d9733e3230e6ccaefadbfd8907cd151221d8af6fdf881b4e09
0f86b1841edb69969c474bf1d71decbc4264697a6a1394e5c70ffaa5cef2f0d0
11e85d065addc6238fe85828a8006cbb9a453d2689ac45fc8f8df26391ed45ea
203c508a5757676ec3185b4d84cda795faf0ea3c751b55049d841bf6674a1f4a
20cb40c59523c122892940d78f4be4946ed9d1e6a434d99f9f1b4d8621552ebb
2231af47e5e4b36fa678a6862ea47562c1c80a69dfe6ff0f78ed31e9d45f2408
2cd88f54beb4cac6f0172308faa2450e28903c29cdf659230fbf0b2b798a77e5
3db389db89bb9e290eeffbaf2bc6e312665699386f00055f57490818d410a20e
44136fa355b3678a1146ad16f7e8649e94fb4fc21fe77e8310c060f61caaff8a
4cecf5572c9a19fabc7d8a565ea671a7f3948265fe4b9a3d38e1d19f1831104a
4dac0026fbfa2615dce30c0af12830863fe885f84387a0147b9e338f548d5d82
4e9ae21bdd47ab5b2f9e929cd5508546a5ee826c1d97a1cbe6025aa37903ebd0
59d0c9e292066e35000342f9fba5a90321ca945ce72b2285820bb8e017df04bf
5c7b44a674eef31957c8f581a5071b4bbe00da066af697e4321de55209d77db1
5e293e7532cd71407b658e5f497bad90a1467ef9d2f4273baf0ef26f8768dd48
5e2dfcdd99fbe63470e85c69591563a7ff90690c3d60f3d333641b6ed672ca6e
6318394f737c66f0e2ccfcd88e3935c6667633a1b95fa29fba2b75431d55eef2
64f64c1e2e00cead6427c05182019fb7c9371ef3e6abdce1982ad2526cad6327
6ddc5a4cda3ccd7c57bad192aa66bdd0e0d987b88835d684de46787bccf131ce
7bea17a80a61ed0f54248b4ffc4c718f7c8ff2619742577a73591d62ce074da8
870a5b3f0ef03d99f1c30bcfcdeddf108e367b6df591eb5851419c5426cf9ab8
870ec6b308ab3e9f6adf8eeb48f604e2b63db81c16e76995d70c779f17ed1a44
882c4596da1475b525d606093cee86aae8fc34febd0fa2dd68010ac52f21e22d
8a44fba94a44e52e8240a0d59b110e39e90255835457ff1f121bbdafaf0425ee
8d138329d6668958413b47c78006f9509dc66f7d84ad98a8777bffea2768c9fe
8d70b3e6badb6973663b398d297bb32eaedd08826a1af98d0a1cfce5324ffce0
995d6e259a04f1ac5c9f536b88f1603836c4066a147a1dd2013d50e7d7cf4be0
9dc8a2df2aeb1376d9ce37280554a9a735638b004bc93fce406af4958dc41d30
a236defd861c4d5c3daff5f76f774fa8207980aa8df746aefa493ada81fbefef
aa82d9dce1e95f879afabf8e919b51b534f850b9f93df6f472d46a14426e0d39
ab5c23a05e39deed14d9d8262b0dce9f024f86105a27196cad37d14a3f516e09
b81324a8025794ccf52484aeaba8607aa33a8930e80938160a430385f5c72bab
d8101878075a1240e6d667c95af0430ec36bb8280e01e281c045255938f97ad5
dc54414fdabae11af71e96713c0b8b3607d0f7be2ce9f73f31c1ab2f4e49fdb1
df2f424495f78cf48886e16478dfea0196ab25d57d4cdcf6c1ea5a719e4424bb
e00e6d30823a3c17cde2c8f5c34c3f9f41201ee3f1ecf4aa68ab3ef685e7e1ec
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
e5d3342a446dc3250cf136835b8a1a4a395d64d52e7861aae0925adda1b393e0
ea12ead71e2ead83370841cac12607b53e84bba92fb9d5e53ce0a31b594afc66
ec788e40da0be6907a13b5fc0537689c9a5052205873b2103ee1f4965df07748
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
fa44fd05d844aace37cbdbec127d8777f41e54121115e6facf6d9a15195df891
fbfb33e468a89d89c340858d3d3e2e448c082e0c72ee3642dfe314ce7aeae4a7
fc23fb8101272a4283de931950ed410e556146496f27ced32869b51b55ee7abb
ff7b52998fd03e350929e0071baf474dd622b4eaa928cf567a8d0a962530e811