
kmsauto.xyz
176.116.0.150
Public Scan
Open in
urlscan Pro
http://kmsauto.xyz/ 4yr old
Effective URL:
https://kmsauto.xyz/ 4yr old
Submission: On August 26 via api (August 26th 2026, 12:47:55 am UTC) from RU — Scanned from NL Go Pro
Only in urlscan Pro
- Select different country locations for Private Scans.
- Use a global network of additional scanning locations and residential IPs for scanning.
- Interact with pages while you are scanning them.
- Download files from remote websites.
- Scan websites on the Tor Network.
Summary
TLS certificate: Issued by YR1 on July 9th 2026. Valid for: 3mo.
This is the only time kmsauto.xyz was scanned on urlscan.io!
urlscan.io Verdict: No classification
Domain & IP information
| IP Address | AS Autonomous System | ||
|---|---|---|---|
| 14 | 176.116.0.150 176.116.0.150 | 200019 (AlexHost ...) (AlexHost ALEXHOST SRL) | |
| 1 | 192.178.183.95 192.178.183.95 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 2 | 88.208.46.222 88.208.46.222 | 39572 (ADVANCEDH...) (ADVANCEDHOSTERS-AS DataWeb Global Group B.V.) | |
| 6 11 | 77.88.21.119 77.88.21.119 | 13238 (YANDEX YA...) (YANDEX YANDEX LLC) | |
| 2 | 142.251.20.94 142.251.20.94 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 24 | 6 |
ASN200019 (AlexHost ALEXHOST SRL, MD)
PTR: mail.incy.cc
| kmsauto.xyz 4yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: lcfraw-in-f95.1e100.net
| fonts.googleapis.com 10yr old |
ASN39572 (ADVANCEDHOSTERS-AS DataWeb Global Group B.V., NL)
| ogffa.net 3yr old | |
| ogfna.net 3yr old |
ASN13238 (YANDEX YANDEX LLC, RU)
PTR: mc.yandex.ru
| mc.yandex.ru 14yr old | |
| mc.yandex.com 13yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: bx-in-f94.1e100.net
| fonts.gstatic.com 10yr old |
| Apex Domain Subdomains |
Transfer | |
|---|---|---|
| 14 |
kmsauto.xyz
kmsauto.xyz 4yr old |
245 KB |
| 7 |
yandex.com
4 redirects
mc.yandex.com — Cisco Umbrella Rank: 11619 13yr old |
5 KB |
| 4 |
yandex.ru
2 redirects
mc.yandex.ru — Cisco Umbrella Rank: 3618 14yr old |
90 KB |
| 2 |
gstatic.com
fonts.gstatic.com — Cisco Umbrella Rank: 33 10yr old |
60 KB |
| 1 |
ogfna.net
ogfna.net 3yr old |
484 B |
| 1 |
ogffa.net
ogffa.net 3yr old |
5 KB |
| 1 |
googleapis.com
fonts.googleapis.com — Cisco Umbrella Rank: 46 10yr old |
1 KB |
| 24 | 7 |
| Domain | Requested by | |
|---|---|---|
| 14 | kmsauto.xyz |
kmsauto.xyz
|
| 8 | mc.yandex.com |
4 redirects
kmsauto.xyz
|
| 4 | mc.yandex.ru |
2 redirects
kmsauto.xyz
|
| 2 | fonts.gstatic.com |
fonts.googleapis.com
|
| 1 | ogfna.net |
ogffa.net
|
| 1 | ogffa.net |
kmsauto.xyz
|
| 1 | fonts.googleapis.com |
kmsauto.xyz
|
| 24 | 7 |
This site contains links to these domains. Also see Links.
| Domain |
|---|
| www.dropbox.com |
| Subject Issuer | Validity | Valid | |
|---|---|---|---|
| kmsauto.xyz YR1 |
2026-07-09 - 2026-10-07 |
3mo | crt.sh |
| upload.video.google.com WE2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| ogffa.net YR1 |
2026-07-08 - 2026-10-06 |
3mo | crt.sh |
| mc.yandex.ru GlobalSign ECC OV SSL CA 2018 |
2026-06-12 - 2026-11-22 |
5mo | crt.sh |
| *.gstatic.com WE2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| ogfna.net YR1 |
2026-07-08 - 2026-10-06 |
3mo | crt.sh |
This page contains 1 frames:
Primary Page:
https://kmsauto.xyz/
Frame ID: 383FFBF0BB825A5BB9F057DA0528FA90
Requests: 32 HTTP requests in this frame
Screenshot
Go Pro
Only in urlscan Pro
Use the Visual Search feature to find pages with visually similar screenshots.
Click for more information
Free trials of urlscan Pro are available.
Page Title
KMSAuto Net — Скачать Активатор Windows и Office 2026Page URL History
Go Pro
Only in urlscan Pro
Search our real-time database of newly observed domains and
hostnames. Pivot on different attributes, and setup keyword alerts for
newly observed domains.
Click for more information
Free trials of urlscan Pro are available.
Show full URLs
-
http://kmsauto.xyz/
HTTP 307
https://kmsauto.xyz/ Page URL
Detected technologies
 WordPress
(CMS)
Expand
Detected patterns
- <link rel=["']stylesheet["'] [^>]+/wp-(?:content|includes)/
- /wp-(?:content|includes)/
 jQuery
(JavaScript libraries)
Expand
Detected patterns
- jquery
 Yandex.Metrika
(Analytics)
Expand
Detected patterns
- mc\.yandex\.ru/metrika/(?:tag|watch)\.js
Page Statistics
1 Outgoing links
Go Pro
Only in urlscan Pro
Effortlessly use any on-page link as a pivot to discover other pages pointing to the exact same destination. Seamlessly trace both specific URLs and broader domains to uncover hidden connection networks and map out backlink relationships with ease.
Click for more information
Free trials of urlscan Pro are available.
These are links going to different origins than the main page.
Title: KMSAuto v1.8.7 Portable скачать бесплатно
Search URL Search Domain Scan URL
Page URL History
This captures the URL locations of the websites, including HTTP redirects and client-side redirects via JavaScript or Meta fields.
-
http://kmsauto.xyz/
HTTP 307
https://kmsauto.xyz/ Page URL
Redirected requests
There were HTTP redirect chains for the following requests:
Request Chain 26- https://mc.yandex.com/sync_cookie_image_check?scid=beb84d6b-4303-7028-4128-ad4b7833e086&cid=94418876 HTTP 302
- https://mc.yandex.ru/sync_cookie_image_start?cid=94418876&redirect_domain=mc.yandex.com&scid=beb84d6b-4303-7028-4128-ad4b7833e086&token=11107.8R2nXlCTCUzE0BhTO6arG7PWge-96Bg5p0L0N1UAlBUsx5_VqDLAU-2Y9_iWZd39.DSnESgqPktXSEsLqJAYpndujVaM%2C HTTP 302
- https://mc.yandex.com/sync_cookie_image_decide?cid=94418876&scid=beb84d6b-4303-7028-4128-ad4b7833e086&token=11107.jYfMFLAy4sSYa5Z_6vaRr9E8e8KLvy_KUk28eeg4qf3ZlsW6MJwaSDwtE-Upw6SEU4zTJhl20HjVIW0UssAX2Gvp0TXKkNJO9ZIGJfG_8Nk%2C.SIWU2Vuj6JihTiK4DW8KtqE-iBA%2C
- https://mc.yandex.com/watch/94418876?wmode=7&page-url=https%3A%2F%2Fkmsauto.xyz%2F&charset=utf-8&uah=chu%0A%22Chromium%22%3Bv%3D%22151%22%2C%22Google%20Chrome%22%3Bv%3D%22151%22%2C%22Not%3DA%3FBrand%22%3Bv%3D%2299%22%0Acha%0Ax86%0Achb%0A64%0Achf%0A151.0.7922.173%0Achl%0A%22Chromium%22%3Bv%3D%22151.0.7922.173%22%2C%22Google%20Chrome%22%3Bv%3D%22151.0.7922.173%22%2C%22Not%3DA%3FBrand%22%3Bv%3D%2299.0.0.0%22%0Achm%0A%3F0%0Achp%0ALinux&browser-info=pv%3A1%3Avf%3A4upiht53cb5sphvcya0ieah7masyqj%3Afu%3A0%3Aen%3Autf-8%3Ala%3Anl-NL%3Av%3A2630%3Acn%3A1%3Adp%3A0%3Als%3A591956938788%3Ahid%3A648858326%3Az%3A120%3Ai%3A20260826024756%3Aet%3A1787705276%3Ac%3A1%3Arn%3A183433613%3Arqn%3A1%3Au%3A1787705276488081709%3Aw%3A1600x1200%3As%3A1600x1200x24%3Ask%3A1%3Afp%3A396%3Awv%3A2%3Ads%3A40%2C57%2C62%2C3%2C2%2C0%2C%2C245%2C1%2C%2C%2C%2C410%3Aco%3A0%3Acpf%3A1%3Ans%3A1787705275261%3Aadb%3A2%3Arqnl%3A1%3Ast%3A1787705276%3At%3AKMSAuto%20Net%20%E2%80%94%20%D0%A1%D0%BA%D0%B0%D1%87%D0%B0%D1%82%D1%8C%20%D0%90%D0%BA%D1%82%D0%B8%D0%B2%D0%B0%D1%82%D0%BE%D1%80%20Windows%20%D0%B8%20Office%202026&t=clt(416)gdpr(14)clc(0-0-0)rqnt(1)aw(1)rcm(1)cdl(na)eco(42009088)wdv(1)wds(0)wdo(0)wdd(0)wdi(0)ti(1) HTTP 302
- https://mc.yandex.com/watch/94418876/1?wmode=7&page-url=https%3A%2F%2Fkmsauto.xyz%2F&charset=utf-8&uah=chu%0A%22Chromium%22%3Bv%3D%22151%22%2C%22Google%20Chrome%22%3Bv%3D%22151%22%2C%22Not%3DA%3FBrand%22%3Bv%3D%2299%22%0Acha%0Ax86%0Achb%0A64%0Achf%0A151.0.7922.173%0Achl%0A%22Chromium%22%3Bv%3D%22151.0.7922.173%22%2C%22Google%20Chrome%22%3Bv%3D%22151.0.7922.173%22%2C%22Not%3DA%3FBrand%22%3Bv%3D%2299.0.0.0%22%0Achm%0A%3F0%0Achp%0ALinux&browser-info=pv%3A1%3Avf%3A4upiht53cb5sphvcya0ieah7masyqj%3Afu%3A0%3Aen%3Autf-8%3Ala%3Anl-NL%3Av%3A2630%3Acn%3A1%3Adp%3A0%3Als%3A591956938788%3Ahid%3A648858326%3Az%3A120%3Ai%3A20260826024756%3Aet%3A1787705276%3Ac%3A1%3Arn%3A183433613%3Arqn%3A1%3Au%3A1787705276488081709%3Aw%3A1600x1200%3As%3A1600x1200x24%3Ask%3A1%3Afp%3A396%3Awv%3A2%3Ads%3A40%2C57%2C62%2C3%2C2%2C0%2C%2C245%2C1%2C%2C%2C%2C410%3Aco%3A0%3Acpf%3A1%3Ans%3A1787705275261%3Aadb%3A2%3Arqnl%3A1%3Ast%3A1787705276%3At%3AKMSAuto%20Net%20%E2%80%94%20%D0%A1%D0%BA%D0%B0%D1%87%D0%B0%D1%82%D1%8C%20%D0%90%D0%BA%D1%82%D0%B8%D0%B2%D0%B0%D1%82%D0%BE%D1%80%20Windows%20%D0%B8%20Office%202026&t=clt%28416%29gdpr%2814%29clc%280-0-0%29rqnt%281%29aw%281%29rcm%281%29cdl%28na%29eco%2842009088%29wdv%281%29wds%280%29wdo%280%29wdd%280%29wdi%280%29ti%281%29&redirnss=1
- https://mc.yandex.com/sync_cookie_image_check_secondary?scid=3f568e18-4098-91a4-6193-e18b751a0c0e&cid=94418876 HTTP 302
- https://mc.yandex.ru/sync_cookie_image_start_secondary?cid=94418876&redirect_domain=mc.yandex.com&scid=3f568e18-4098-91a4-6193-e18b751a0c0e&token=11107.aZTLay5vyaJ-OiLk_rCNMn8MHmM4BYaHCUiwgQPxREpFupmvzQg01Ng4fAovMsHV.PvVDsaUqBMN7G8GtKYZ-WNeIxBA%2C HTTP 302
- https://mc.yandex.com/sync_cookie_image_decide_secondary?cid=94418876&scid=3f568e18-4098-91a4-6193-e18b751a0c0e&token=11107.UCAAryAbiGaZw3GrcWwm4E4tm_ssjy3ad7rZ6YVZ_AvUpR2bzmGfMYCmXsvmAQ0arHmmZFzX1aKk0tXBGQmq8pPMmYjIrXz7V3lybezwwB4%2C._qtFdpDpeGYiD4yxOLMyVPDP9s4%2C HTTP 302
- https://mc.yandex.ru/sync_cookie_image_finish_secondary?cid=94418876&redirect_domain=mc.yandex.com&scid=3f568e18-4098-91a4-6193-e18b751a0c0e&token=11107.ROMRohKet7Y7IIw6Ex1-9L1uoxGodRk5C1lFeQwDjaJ4G9955-eiI-Tg4Zr3k8YfK7fqP0HhOsEHS_AOrI9qC070QWsu_7vKzcsDH2vgSyUPXRtoXgMIIeC7ENzMuqmvS4nIfRFZAGqZZAuky9tV9h5R9m_djzpqEZzZRrH8-P5aAljQboQC6FO5EOJ42V33p8r-hRDHyVi2-M8o3LLnEg%2C%2C.IyAzmfG0CZBXZQ0EjFitgyi-Yig%2C
24 HTTP transactions
Go Pro
Only in urlscan Pro
Inspect WebSocket connections, examine POST data effortlessly, and track overlap counts in real time. Features live search and filtering across all HTTP output, complete with full response metadata for deep analysis.
Click for more information
Free trials of urlscan Pro are available.
8 data transactions
| Method Protocol |
Status | Resource Path |
Size x-fer |
Time Latency |
Type MIME-Type |
IP Location |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
|
GET H2 |
200 |
Primary Request
/
Show response
kmsauto.xyz/ Redirect Chain
|
51 KB 14 KB |
160ms
63ms |
Document
text/html |
176.116.0.150 AlexHost ALEXHOST... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
style.min.css
kmsauto.xyz/wp-includes/css/dist/block-library/ |
137 KB 23 KB |
37ms
35ms |
Stylesheet
text/css |
176.116.0.150 AlexHost ALEXHOST... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
css
fonts.googleapis.com/ |
6 KB 1 KB |
108ms
35ms |
Stylesheet
text/css |
192.178.183.95 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
style.min.css
kmsauto.xyz/wp-content/themes/reboot/assets/css/ |
230 KB 47 KB |
58ms
56ms |
Stylesheet
text/css |
176.116.0.150 AlexHost ALEXHOST... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
jquery.min.js
Show response
kmsauto.xyz/wp-includes/js/jquery/ |
86 KB 33 KB |
72ms
70ms |
Script
application/javascript |
176.116.0.150 AlexHost ALEXHOST... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
wpshop-core.ttf
kmsauto.xyz/wp-content/themes/reboot/assets/fonts/ |
57 KB 26 KB |
95ms
94ms |
Font
x-font/ttf |
176.116.0.150 AlexHost ALEXHOST... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
%D0%B8%D0%B7%D0%BE%D0%B1%D1%80%D0%B0%D0%B6%D0%B5%D0%BD%D0%B8%D0%B5.png
kmsauto.xyz/wp-content/uploads/2024/04/ |
16 KB 16 KB |
80ms
79ms |
Image
image/png |
176.116.0.150 AlexHost ALEXHOST... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
%D0%B8%D0%B7%D0%BE%D0%B1%D1%80%D0%B0%D0%B6%D0%B5%D0%BD%D0%B8%D0%B5-1.png
kmsauto.xyz/wp-content/uploads/2024/04/ |
25 KB 25 KB |
87ms
86ms |
Image
image/png |
176.116.0.150 AlexHost ALEXHOST... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
%D0%B8%D0%B7%D0%BE%D0%B1%D1%80%D0%B0%D0%B6%D0%B5%D0%BD%D0%B8%D0%B5-2.png
kmsauto.xyz/wp-content/uploads/2024/04/ |
31 KB 31 KB |
91ms
90ms |
Image
image/png |
176.116.0.150 AlexHost ALEXHOST... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
scripts.min.js
Show response
kmsauto.xyz/wp-content/themes/reboot/assets/js/ |
53 KB 11 KB |
17ms
16ms |
Script
application/javascript |
176.116.0.150 AlexHost ALEXHOST... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
comment-reply.min.js
Show response
kmsauto.xyz/wp-includes/js/ |
3 KB 2 KB |
28ms
28ms |
Script
application/javascript |
176.116.0.150 AlexHost ALEXHOST... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
llc_scroll.min.js
Show response
kmsauto.xyz/wp-content/plugins/lazy-load-for-comments/public/js/ |
888 B 654 B |
18ms
17ms |
Script
application/javascript |
176.116.0.150 AlexHost ALEXHOST... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
getcode
Show response
ogffa.net/sm/ |
20 KB 5 KB |
86ms
26ms |
Script
text/javascript |
88.208.46.222 ADVANCEDHOSTERS-A... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET DATA |
200 OK |
truncated
/ |
2 KB 0 |
Image
image/gif |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
tag.js
Show response
mc.yandex.ru/metrika/ |
270 KB 89 KB |
302ms
139ms |
Script
application/javascript |
77.88.21.119 YANDEX YANDEX LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET DATA |
200 OK |
truncated
/ |
969 B 0 |
Image
image/svg+xml |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET DATA |
200 OK |
truncated
/ |
442 B 0 |
Image
image/svg+xml |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET DATA |
200 OK |
truncated
/ |
290 B 0 |
Image
image/svg+xml |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET DATA |
200 OK |
truncated
/ |
626 B 0 |
Image
image/svg+xml |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET DATA |
200 OK |
truncated
/ |
544 B 0 |
Image
image/svg+xml |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET DATA |
200 OK |
truncated
/ |
1 KB 0 |
Image
image/svg+xml |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET DATA |
200 OK |
truncated
/ |
477 B 0 |
Image
image/png |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
JTUSjIg1_i6t8kCHKm459W1hyzbi.woff2
fonts.gstatic.com/s/montserrat/v31/ |
23 KB 23 KB |
60ms
25ms |
Font
font/woff2 |
142.251.20.94 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
JTUSjIg1_i6t8kCHKm459Wlhyw.woff2
fonts.gstatic.com/s/montserrat/v31/ |
37 KB 37 KB |
66ms
31ms |
Font
font/woff2 |
142.251.20.94 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
cropped-pngwing.com_.png
kmsauto.xyz/wp-content/uploads/2023/07/ |
16 KB 16 KB |
15ms
15ms |
Image
image/png |
176.116.0.150 AlexHost ALEXHOST... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
stat
Show response
ogfna.net/sm/ |
0 484 B |
170ms
83ms |
XHR
text/html |
88.208.46.222 ADVANCEDHOSTERS-A... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
admin-ajax.php
Show response
kmsauto.xyz/wp-admin/ |
49 B 450 B |
208ms
208ms |
XHR
application/json |
176.116.0.150 AlexHost ALEXHOST... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
sync_cookie_image_decide
mc.yandex.com/ Redirect Chain
|
43 B 66 B |
70ms
70ms |
Image
image/gif |
77.88.21.119 YANDEX YANDEX LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
advert.gif
mc.yandex.com/metrika/ |
43 B 186 B |
131ms
131ms |
Image
image/gif |
77.88.21.119 YANDEX YANDEX LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
1
Show response
mc.yandex.com/watch/94418876/ Redirect Chain
|
738 B 1 KB |
137ms
137ms |
Fetch
application/json |
77.88.21.119 YANDEX YANDEX LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
cropped-cropped-pngwing.com_-32x32.png
kmsauto.xyz/wp-content/uploads/2024/02/ |
833 B 1005 B |
14ms
14ms |
Other
image/png |
176.116.0.150 AlexHost ALEXHOST... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
sync_cookie_image_finish_secondary
mc.yandex.ru/ Redirect Chain
|
43 B 403 B |
137ms
136ms |
Image
image/gif |
77.88.21.119 YANDEX YANDEX LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||


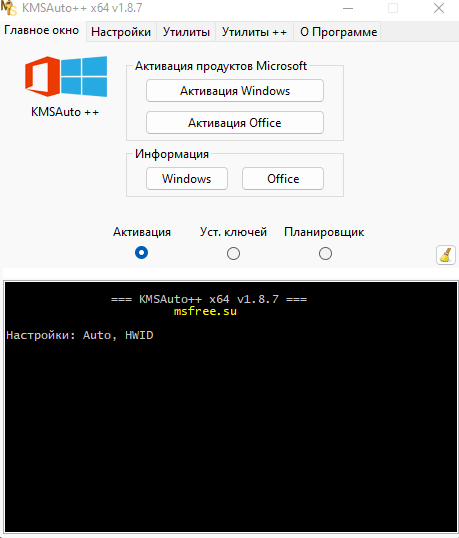


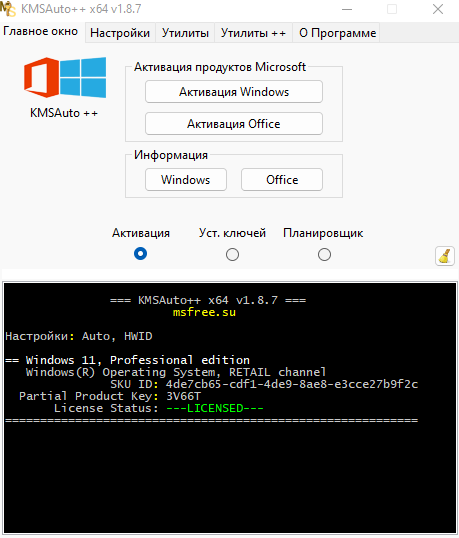


Verdicts & Comments Add Verdict or Comment
22 JavaScript Window variables
Go Pro
Only in urlscan Pro
Inspect and pivot on JavaScript variables, identifiers, and other key site metadata data with urlscan Pro. Reveal and search on client-side frameworks, runtime variables, and custom values.
Click for more information
Free trials of urlscan Pro are available.
These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.
function| jQuery function| ym object| pseudo_links object| settings_array object| wps_ajax object| wpshop_views_counter_params boolean| isMobile boolean| isSearchBot object| VK object| ODKL object| _goodshare object| llcstrings object| addComment function| setCookie function| getCookie function| eraseCookie function| smmakeid function| addScript function| main string| top_menu_mobile_position object| Ya object| yaCounter9441887620 Cookies
Go Pro
Only in urlscan Pro
Review, search, and pivot on browser cookies and persistence site data to see how a site tracks users and keeps sessions alive across visits.
Click for more information
Free trials of urlscan Pro are available.
Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.
| Domain/Path | Expires | Name / Value | |||
|---|---|---|---|---|---|
| kmsauto.xyz/ | 1970-01-21 16:36:31 |
Name: smid Value: YTfC8i1I |
|||
| .yandex.ru/ | 1970-01-22 02:11:05 |
Name: bh Value: EkEiQ2hyb21pdW0iO3Y9IjE1MSIsICJHb29nbGUgQ2hyb21lIjt2PSIxNTEiLCAiTm90PUE/QnJhbmQiO3Y9Ijk5IioCPzA6ByJMaW51eCJgu++41AZqGdzK6YgO8qy3pQv7+vDnDev//fYPwf7Phwg= |
|||
| .kmsauto.xyz/ | 1970-01-22 01:20:41 |
Name: _ym_uid Value: 1787705276488081709 |
|||
| .kmsauto.xyz/ | 1970-01-22 01:20:41 |
Name: _ym_d Value: 1787705276 |
|||
| .mc.yandex.com/ | 1970-01-21 16:35:05 |
Name: sync_cookie_csrf Value: 1065573781fake |
|||
| .kmsauto.xyz/ | 1970-01-21 16:36:17 |
Name: _ym_isad Value: 2 |
|||
| .mc.yandex.ru/ | 1970-01-21 16:35:05 |
Name: sync_cookie_csrf Value: 3647618439fake |
|||
| mc.yandex.com/ | 1969-12-31 23:59:59 |
Name: yabs-sid Value: 2521754051787705276 |
|||
| .yandex.com/ | 1970-01-22 02:11:05 |
Name: i Value: 42NO+Lolv4D62ScXtoL3G1hxE7za62tlyvdXgKF9MpnvHWPaXIW5eMbFD7qUrk9Q6V1HzYuwIaNdrPlwz0F0bPBpzDM= |
|||
| .yandex.com/ | 1970-01-22 02:11:05 |
Name: yandexuid Value: 2730405301787705276 |
|||
| .yandex.com/ | 1970-01-22 01:20:41 |
Name: yuidss Value: 2730405301787705276 |
|||
| .yandex.com/ | 1970-01-22 01:20:41 |
Name: ymex Value: 1819241276.yrts.1787705276#1819241276.yrtsi.1787705276 |
|||
| .yandex.com/ | 1970-01-22 01:20:41 |
Name: receive-cookie-deprecation Value: 1 |
|||
| .yandex.com/ | 1970-01-22 02:11:05 |
Name: bh Value: EkEiQ2hyb21pdW0iO3Y9IjE1MSIsICJHb29nbGUgQ2hyb21lIjt2PSIxNTEiLCAiTm90PUE/QnJhbmQiO3Y9Ijk5IhoDeDg2Ig4xNTEuMC43OTIyLjE3MyoCPzA6ByJMaW51eCJKAjY0UlsiQ2hyb21pdW0iO3Y9IjE1MS4wLjc5MjIuMTczIiwiR29vZ2xlIENocm9tZSI7dj0iMTUxLjAuNzkyMi4xNzMiLCJOb3Q9QT9CcmFuZCI7dj0iOTkuMC4wLjAiYLzvuNQGahncyumIDvKst6UL+/rw5w3r//32D8H+z4cI |
|||
| .mc.yandex.com/ | 1970-01-21 16:35:05 |
Name: sync_cookie_csrf_secondary Value: 1893852425fake |
|||
| .mc.yandex.ru/ | 1970-01-21 16:35:05 |
Name: sync_cookie_csrf_secondary Value: 3751066638fake |
|||
| .mc.yandex.com/ | 1970-01-21 16:36:31 |
Name: sync_cookie_ok_secondary Value: synced |
|||
| .yandex.ru/ | 1970-01-22 02:11:05 |
Name: yandexuid Value: 2730405301787705276 |
|||
| .yandex.ru/ | 1970-01-22 02:11:05 |
Name: yuidss Value: 2730405301787705276 |
|||
| .yandex.ru/ | 1970-01-22 02:11:05 |
Name: i Value: 42NO+Lolv4D62ScXtoL3G1hxE7za62tlyvdXgKF9MpnvHWPaXIW5eMbFD7qUrk9Q6V1HzYuwIaNdrPlwz0F0bPBpzDM= |
Security Headers
This page lists any security headers set by the main page. If you want to understand what these mean and how to use them, head on over to this page
| Header | Value |
|---|---|
| Strict-Transport-Security | max-age=31536000 |
Indicators
This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.
fonts.googleapis.com
fonts.gstatic.com
kmsauto.xyz
mc.yandex.com
mc.yandex.ru
ogffa.net
ogfna.net
142.251.20.94
176.116.0.150
192.178.183.95
77.88.21.119
88.208.46.222
06b16db7a969135d48d38c49183be7fb88d4452e2a3011957c7851941f4e4879
0fa883123cb7c36c46a3f549a3c4d066044c3b5947f3017835a47e8e82eef4f1
17df1f2891553baf6c74c4eef8cd0dd9fb73a5669f9f89d67183a8bfe41acfd2
19ea033870b6c8315064d792b128439adb831f241a61457be781a830d11ff625
22c5f0bc809ec23dc5688312e96924dccd7e4b76af11be352d396c7c84173079
255df06063ef8b4f994c1ae9d232d7c4f27c95b853a68fd9c03e31f4dd6b0031
289dacff0405fab821ad733fa6635ead27ba807b89e1fb61be1f431fa58f3195
2d51fd87cceb144213323d6aa0dd510cbb8e8df164b92f88d00a821c904a81e5
3f71fcd8a4edd9edf1aa6a92cf0e3d265d2266e73952b3a79d3d95ceba8195f1
401503518894f575673732c689a7885c78bb615900c0c3f726765eb4ce6aa799
4192547933c47032776c86cc04805a86655e4580d0c82b46787a120fcd96c146
548f2d6f4d0d820c6c5ffbeffcbd7f0e73193e2932eefe542accc84762deec87
67d81c1bcf1c532398f80ca729d4ca0dc01fe141632851c153316c932fe7fc0f
6bfd33239aeedf89d3e3708614a8b890b6f20d9b3ebface16f40656662e620c1
6e9cca040634f071c068f7f483dfeef82d8589b4082c8cbdc5301951647ba71b
81511e960d89082868da3036ac2ba90cf8fd027102aac32abe1b82e72b1c1591
84c5402c3806c020dc53b7bb3b53097282089e8cdab24b50de7854217f91c47d
8d74b7089a68f822f535c265ed9b4faf167417defaeed5985d00f7d1f8d83007
932d52aad7a8b40411e4c760cd65aafbffa11c4f417f8491e6201f3a52c8d2c5
973408bd1a1da181c7eaa9293c0cd095f3836a76b626bc76af21e1cd96b5dcde
9dab7e5d8a3648766c93cffe76d8f64d51934c074395764672a890b02f69095d
a187b077090fe8ae3fd2d7496aabbeae604819c718a282e0afc92df72b450766
ac042db46d539943a9a18ace267c4dda7490bb7566ab3b7f69f1433b241c3582
b6ddbedb43987add2f27f07fe2d24f98f58c76a5e67d7f283eba454e00fcd651
cb6f2d32c49d1c2b25e9ffc9aaafa3f83075346c01bcd4ae6eb187392a4292cf
d5aab9ecebd2bc2f003980fdde59b97aad0fd105312d99fa50fcab580099aaf3
dda8518b79528a09d3a8ee2eda6a550b5873d61104ee5535adc7557f9bff6b26
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
f2cc60607c1d407e194dddc628e9fde74e56b9a60c4ba39d6b17a5e2629c83fb
f4bacc381f6f5c283883955c53ded4d8f0bc624076abfbcf1eab973045a30c60