
picasasupport.pages.dev
188.114.97.3
Public Scan
Open in
urlscan Pro
https://picasasupport.pages.dev/ 2yr old
Submission: On August 28 via automatic, source certstream-suspicious (August 28th 2026, 10:45:36 am UTC) — Scanned from DE Go Pro
Only in urlscan Pro
- Select different country locations for Private Scans.
- Use a global network of additional scanning locations and residential IPs for scanning.
- Interact with pages while you are scanning them.
- Download files from remote websites.
- Scan websites on the Tor Network.
Summary
TLS certificate: Issued by WE1 on July 9th 2026. Valid for: 3mo.
This is the only time picasasupport.pages.dev was scanned on urlscan.io!
urlscan.io Verdict: No classification
Domain & IP information
| IP Address | AS Autonomous System | ||
|---|---|---|---|
| 2 | 188.114.97.3 188.114.97.3 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 2 | 104.18.10.207 104.18.10.207 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 2a00:1450:400... 2a00:1450:4001:c1f::5f | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 2a04:4e42::411 2a04:4e42::411 | 54113 (FASTLY) (FASTLY - Fastly) | |
| 1 | 23.81.204.137 23.81.204.137 | 19148 (LEASEWEB-...) (LEASEWEB-USA-PHX - Leaseweb USA) | |
| 1 | 154.9.154.230 154.9.154.230 | 64249 (ENDOFFICE) (ENDOFFICE - Charles River Operation) | |
| 3 | 2a00:1450:400... 2a00:1450:4001:c25::77 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 5 | 2a02:26f0:350... 2a02:26f0:3500:12::1730:1793 | 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.) | |
| 1 | 192.0.77.2 192.0.77.2 | 2635 (AUTOMATTIC) (AUTOMATTIC - Automattic) | |
| 1 | 2606:4700:10:... 2606:4700:10::ac42:ad14 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 168.119.121.23 168.119.121.23 | 24940 (HETZNER-A...) (HETZNER-AS Hetzner Online GmbH) | |
| 1 | 2606:4700:20:... 2606:4700:20::681a:4c7 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 185.126.218.147 185.126.218.147 | 219450 (VOYAR VOY...) (VOYAR VOYAR VERIMERKEZI TEKNOLOJILERI LTD. STI) | |
| 1 | 2606:4700:303... 2606:4700:3037::ac43:867c | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 2400:52e0:1e0... 2400:52e0:1e00:2::1329:1 | 60068 (CDN77 Dat...) (CDN77 Datacamp Limited) | |
| 1 | 2a04:4e42:200... 2a04:4e42:200::720 | 54113 (FASTLY) (FASTLY - Fastly) | |
| 1 | 151.101.193.91 151.101.193.91 | 54113 (FASTLY) (FASTLY - Fastly) | |
| 2 | 142.251.20.119 142.251.20.119 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 142.132.217.230 142.132.217.230 | 24940 (HETZNER-A...) (HETZNER-AS Hetzner Online GmbH) | |
| 1 | 2a00:1450:400... 2a00:1450:4001:c17::84 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 2606:4700:20:... 2606:4700:20::681a:c6d | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 172.67.174.33 172.67.174.33 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 2a04:4e42:400... 2a04:4e42:400::311 | 54113 (FASTLY) (FASTLY - Fastly) | |
| 1 | 3.167.227.35 3.167.227.35 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 1 1 | 198.58.126.96 198.58.126.96 | 63949 (AKAMAI-LI...) (AKAMAI-LINODE-AP - Akamai Connected Cloud) | |
| 1 | 2606:4700:10:... 2606:4700:10::6814:11cb | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 10 | 2620:1ec:33::10 2620:1ec:33::10 | 8075 (MICROSOFT...) (MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation) | |
| 55 | 27 |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| picasasupport.pages.dev 2yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| stackpath.bootstrapcdn.com 8yr old | |
| maxcdn.bootstrapcdn.com 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
| fonts.googleapis.com 10yr old |
ASN19148 (LEASEWEB-USA-PHX - Leaseweb USA, Inc., US)
| data-recovery.wiki 6yr old |
ASN64249 (ENDOFFICE - Charles River Operation, US)
| www.izitru.com 6yr old |
ASN15169 (GOOGLE - Google LLC, US)
| i.ytimg.com 10yr old |
ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL)
| i.pinimg.com 10yr old |
ASN2635 (AUTOMATTIC - Automattic, Inc, US)
PTR: i1.wp.com
| i0.wp.com 10yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| www.pcgamesn.com 9yr old |
ASN24940 (HETZNER-AS Hetzner Online GmbH, DE)
PTR: static.23.121.119.168.clients.your-server.de
| www.uzaktanegitim.com 13yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| img.tamindir.com 9yr old |
ASN219450 (VOYAR VOYAR VERIMERKEZI TEKNOLOJILERI LTD. STI, TR)
PTR: sunucu.webzagor.com
| trendkiz.com 12yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| pocketranger.com 13yr old |
ASN60068 (CDN77 Datacamp Limited, GB)
| peaceofmindtransitions.b-cdn.net 2yr old |
ASN54113 (FASTLY - Fastly, Inc., US)
| gdm-catalog-fmapi-prod.imgix.net 6yr old |
ASN54113 (FASTLY - Fastly, Inc., US)
| s3-media4.ak.yelpcdn.com 8yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: bx-in-f119.1e100.net
| i.ytimg.com 10yr old |
ASN24940 (HETZNER-AS Hetzner Online GmbH, DE)
PTR: mail.bramjnaa.com
| bramjnaa.com 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
| 2.bp.blogspot.com 10yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| editor.analyticsvidhya.com 6yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| blog.vilmatech.com 7yr old |
ASN54113 (FASTLY - Fastly, Inc., US)
| assetsio.reedpopcdn.com 4yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-3-167-227-35.fra60.r.cloudfront.net
| media.cntraveler.com 9yr old |
ASN63949 (AKAMAI-LINODE-AP - Akamai Connected Cloud, SG)
PTR: li690-96.members.linode.com
| s.getwinpcsoft.com 8yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| img.informer.com 9yr old |
ASN8075 (MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation, US)
| tse2.mm.bing.net 10yr old | |
| tse4.mm.bing.net 10yr old | |
| tse1.mm.bing.net 10yr old | |
| tse3.mm.bing.net 10yr old |
| Apex Domain Subdomains |
Transfer | |
|---|---|---|
| 10 |
bing.net
tse2.mm.bing.net — Cisco Umbrella Rank: 8701 10yr old tse4.mm.bing.net — Cisco Umbrella Rank: 8746 10yr old tse1.mm.bing.net — Cisco Umbrella Rank: 4817 10yr old tse3.mm.bing.net — Cisco Umbrella Rank: 8579 10yr old |
92 KB |
| 5 |
pinimg.com
i.pinimg.com — Cisco Umbrella Rank: 2184 10yr old |
1 MB |
| 5 |
ytimg.com
i.ytimg.com — Cisco Umbrella Rank: 126 10yr old |
316 KB |
| 2 |
bootstrapcdn.com
stackpath.bootstrapcdn.com — Cisco Umbrella Rank: 3832 8yr old maxcdn.bootstrapcdn.com — Cisco Umbrella Rank: 1454 10yr old |
36 KB |
| 2 |
pages.dev
picasasupport.pages.dev 2yr old |
14 KB |
| 1 |
informer.com
img.informer.com — Cisco Umbrella Rank: 433816 9yr old |
37 KB |
| 1 |
getwinpcsoft.com
1 redirects
s.getwinpcsoft.com 8yr old |
316 B |
| 1 |
cntraveler.com
media.cntraveler.com — Cisco Umbrella Rank: 174466 9yr old |
373 KB |
| 1 |
reedpopcdn.com
assetsio.reedpopcdn.com 4yr old |
103 KB |
| 1 |
vilmatech.com
blog.vilmatech.com 7yr old |
72 KB |
| 1 |
analyticsvidhya.com
editor.analyticsvidhya.com 6yr old |
491 KB |
| 1 |
blogspot.com
2.bp.blogspot.com — Cisco Umbrella Rank: 37223 10yr old |
698 KB |
| 1 |
bramjnaa.com
bramjnaa.com 10yr old |
72 KB |
| 1 |
yelpcdn.com
s3-media4.ak.yelpcdn.com 8yr old |
41 KB |
| 1 |
imgix.net
gdm-catalog-fmapi-prod.imgix.net — Cisco Umbrella Rank: 286510 6yr old |
127 KB |
| 1 |
b-cdn.net
peaceofmindtransitions.b-cdn.net 2yr old |
178 KB |
| 1 |
pocketranger.com
pocketranger.com 13yr old |
19 KB |
| 1 |
trendkiz.com
trendkiz.com 12yr old |
138 KB |
| 1 |
tamindir.com
img.tamindir.com 9yr old |
44 KB |
| 1 |
uzaktanegitim.com
www.uzaktanegitim.com 13yr old |
59 KB |
| 1 |
pcgamesn.com
www.pcgamesn.com — Cisco Umbrella Rank: 71407 9yr old |
277 KB |
| 1 |
wp.com
i0.wp.com — Cisco Umbrella Rank: 4034 10yr old |
20 KB |
| 1 |
izitru.com
www.izitru.com 6yr old |
135 KB |
| 1 |
data-recovery.wiki
data-recovery.wiki 6yr old |
185 KB |
| 1 |
jquery.com
code.jquery.com — Cisco Umbrella Rank: 830 13yr old |
24 KB |
| 1 |
googleapis.com
fonts.googleapis.com — Cisco Umbrella Rank: 50 10yr old |
1022 B |
| 0 |
247tecno.com
Failed
247tecno.com Failed 7yr old |
|
| 0 |
romsx.com
Failed
romsx.com Failed 8yr old |
|
| 0 |
allpcworld.com
Failed
allpcworld.com Failed 9yr old |
|
| 0 |
compressjpeg.online
Failed
compressjpeg.online Failed 9yr old |
|
| 0 |
elerniam.com
Failed
www.elerniam.com Failed 8yr old |
|
| 0 |
neurotechnologycloud.com
Failed
neurotechnologycloud.com Failed 4mo old |
|
| 0 |
freelatestjob.in
Failed
freelatestjob.in Failed 5yr old |
|
| 0 |
neolifeclinica.com.br
Failed
neolifeclinica.com.br Failed 9yr old |
|
| 0 |
hch.tv
Failed
hch.tv Failed 10yr old |
|
| 0 |
appsforwin10.com
Failed
appsforwin10.com Failed 8yr old |
|
| 0 |
antivirus.my.id
Failed
antivirus.my.id Failed 6yr old |
|
| 55 | 37 |
| Domain | Requested by | |
|---|---|---|
| 5 | tse2.mm.bing.net |
picasasupport.pages.dev
|
| 5 | i.pinimg.com |
picasasupport.pages.dev
|
| 5 | i.ytimg.com |
picasasupport.pages.dev
|
| 3 | tse4.mm.bing.net |
picasasupport.pages.dev
|
| 2 | picasasupport.pages.dev | |
| 1 | tse3.mm.bing.net |
picasasupport.pages.dev
|
| 1 | tse1.mm.bing.net |
picasasupport.pages.dev
|
| 1 | img.informer.com |
picasasupport.pages.dev
|
| 1 | s.getwinpcsoft.com | 1 redirects |
| 1 | media.cntraveler.com |
picasasupport.pages.dev
|
| 1 | assetsio.reedpopcdn.com |
picasasupport.pages.dev
|
| 1 | blog.vilmatech.com |
picasasupport.pages.dev
|
| 1 | editor.analyticsvidhya.com |
picasasupport.pages.dev
|
| 1 | 2.bp.blogspot.com |
picasasupport.pages.dev
|
| 1 | bramjnaa.com |
picasasupport.pages.dev
|
| 1 | s3-media4.ak.yelpcdn.com |
picasasupport.pages.dev
|
| 1 | gdm-catalog-fmapi-prod.imgix.net |
picasasupport.pages.dev
|
| 1 | peaceofmindtransitions.b-cdn.net |
picasasupport.pages.dev
|
| 1 | pocketranger.com |
picasasupport.pages.dev
|
| 1 | trendkiz.com |
picasasupport.pages.dev
|
| 1 | img.tamindir.com |
picasasupport.pages.dev
|
| 1 | www.uzaktanegitim.com |
picasasupport.pages.dev
|
| 1 | www.pcgamesn.com |
picasasupport.pages.dev
|
| 1 | i0.wp.com |
picasasupport.pages.dev
|
| 1 | www.izitru.com |
picasasupport.pages.dev
|
| 1 | data-recovery.wiki |
picasasupport.pages.dev
|
| 1 | maxcdn.bootstrapcdn.com |
picasasupport.pages.dev
|
| 1 | code.jquery.com |
picasasupport.pages.dev
|
| 1 | fonts.googleapis.com |
picasasupport.pages.dev
|
| 1 | stackpath.bootstrapcdn.com |
picasasupport.pages.dev
|
| 0 | 247tecno.com Failed |
picasasupport.pages.dev
|
| 0 | romsx.com Failed |
picasasupport.pages.dev
|
| 0 | allpcworld.com Failed |
picasasupport.pages.dev
|
| 0 | compressjpeg.online Failed |
picasasupport.pages.dev
|
| 0 | www.elerniam.com Failed |
picasasupport.pages.dev
|
| 0 | neurotechnologycloud.com Failed |
picasasupport.pages.dev
|
| 0 | freelatestjob.in Failed |
picasasupport.pages.dev
|
| 0 | neolifeclinica.com.br Failed |
picasasupport.pages.dev
|
| 0 | hch.tv Failed |
picasasupport.pages.dev
|
| 0 | appsforwin10.com Failed |
picasasupport.pages.dev
|
| 0 | antivirus.my.id Failed |
picasasupport.pages.dev
|
| 55 | 41 |
This site contains no links.
| Subject Issuer | Validity | Valid | |
|---|---|---|---|
| picasasupport.pages.dev WE1 |
2026-07-09 - 2026-10-08 |
3mo | crt.sh |
| bootstrapcdn.com WE1 |
2026-07-01 - 2026-09-29 |
3mo | crt.sh |
| upload.video.google.com WE2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| *.jquery.com Sectigo Public Server Authentication CA DV E36 |
2026-05-20 - 2026-12-04 |
7mo | crt.sh |
| www.data-recovery.wiki YR2 |
2026-08-06 - 2026-11-04 |
3mo | crt.sh |
| izitru.com YR2 |
2026-08-20 - 2026-11-18 |
3mo | crt.sh |
| edgestatic.com WR2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| *.pinimg.com DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2026-06-22 - 2027-01-06 |
7mo | crt.sh |
| wp.com YE2 |
2026-08-01 - 2026-10-30 |
3mo | crt.sh |
| pcgamesn.com YE2 |
2026-08-11 - 2026-11-09 |
3mo | crt.sh |
| uzaktanegitim.com YR1 |
2026-08-06 - 2026-11-04 |
3mo | crt.sh |
| tamindir.com WE1 |
2026-08-17 - 2026-11-15 |
3mo | crt.sh |
| *.trendkiz.com YE2 |
2026-07-02 - 2026-09-30 |
3mo | crt.sh |
| pocketranger.com WE1 |
2026-07-31 - 2026-10-29 |
3mo | crt.sh |
| *.b-cdn.net Sectigo Public Server Authentication CA DV R36 |
2025-11-06 - 2026-11-11 |
1yr | crt.sh |
| *.imgix.com GlobalSign Atlas R46 DV TLS CA 2026 Q3 |
2026-08-19 - 2027-03-06 |
7mo | crt.sh |
| s3-media.ak.yelpcdn.com YR2 |
2026-07-03 - 2026-10-01 |
3mo | crt.sh |
| bramjnaa.com YE1 |
2026-08-11 - 2026-11-09 |
3mo | crt.sh |
| misc-sni.blogspot.com WE2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| analyticsvidhya.com WE1 |
2026-08-17 - 2026-11-15 |
3mo | crt.sh |
| vilmatech.com WE1 |
2026-08-08 - 2026-11-06 |
3mo | crt.sh |
| *.reedpopcdn.com YR2 |
2026-08-03 - 2026-11-01 |
3mo | crt.sh |
| vulcan.conde.digital Amazon RSA 2048 M04 |
2026-08-26 - 2027-03-11 |
7mo | crt.sh |
| *.mm.bing.net Microsoft TLS G2 RSA CA OCSP 04 |
2026-07-14 - 2027-01-10 |
6mo | crt.sh |
This page contains 1 frames:
Primary Page:
https://picasasupport.pages.dev/
Frame ID: B8438129F0238A51B397E7544C0D6AF2
Requests: 55 HTTP requests in this frame
Screenshot
Go Pro
Only in urlscan Pro
Use the Visual Search feature to find pages with visually similar screenshots.
Click for more information
Free trials of urlscan Pro are available.
Page Title
Picasa SupportDetected technologies
 WordPress
(CMS)
Expand
Detected patterns
- /wp-(?:content|includes)/
 Bootstrap
(UI frameworks)
Expand
Detected patterns
- <link[^>]* href=[^>]*?bootstrap(?:[^>]*?([0-9a-fA-F]{7,40}|[\d]+(?:.[\d]+(?:.[\d]+)?)?)|)[^>-]*?(?:\.min)?\.css
- (?:/|-)bootstrap(?:[^/]*?([0-9a-fA-F]{7,40}|[\d]+(?:\.[\d]+(?:\.[\d]+)?)?)|)[^/]*?(?:\.min)?\.js
HSTS (Security) Expand
Detected patterns
- ^https://[\w\d\.\-]+(?:\.dev)(?:/.+||/)$
 jQuery
(JavaScript libraries)
Expand
Detected patterns
- jquery
- /jquery(?:-(\d+\.\d+\.\d+))[/.-]
jQuery CDN
(CDN)
Expand
Detected patterns
- code\.jquery\.com/
Page Statistics
0 Outgoing links
Go Pro
Only in urlscan Pro
Effortlessly use any on-page link as a pivot to discover other pages pointing to the exact same destination. Seamlessly trace both specific URLs and broader domains to uncover hidden connection networks and map out backlink relationships with ease.
Click for more information
Free trials of urlscan Pro are available.
These are links going to different origins than the main page.
Redirected requests
There were HTTP redirect chains for the following requests:
Request Chain 30- https://skybiometry.com/wp-content/uploads/2022/06/Best-Face-Recognition-Software.jpg HTTP 302
- https://www.neurotechnologycloud.com/ HTTP 301
- https://neurotechnologycloud.com/
- https://romsx.com/wp-content/uploads/2020/12/20201225_125518.jpg HTTP 302
- https://romsx.com/cgi-sys/suspendedpage.cgi
- https://s.getwinpcsoft.com/screenshots/1801/1801568_1.gif HTTP 301
- https://img.informer.com/screenshots/1801/1801568_1.gif
55 HTTP transactions
Go Pro
Only in urlscan Pro
Inspect WebSocket connections, examine POST data effortlessly, and track overlap counts in real time. Features live search and filtering across all HTTP output, complete with full response metadata for deep analysis.
Click for more information
Free trials of urlscan Pro are available.
0 data transactions
| Method Protocol |
Status | Resource Path |
Size x-fer |
Time Latency |
Type MIME-Type |
IP Location |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
|
GET H3 |
200 |
Primary Request
/
Show response
picasasupport.pages.dev/ |
30 KB 7 KB |
74ms
40ms |
Document
text/html |
188.114.97.3 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
bootstrap.min.css
stackpath.bootstrapcdn.com/bootstrap/4.1.3/css/ |
138 KB 22 KB |
53ms
31ms |
Stylesheet
text/css |
104.18.10.207 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
css
fonts.googleapis.com/ |
2 KB 1022 B |
140ms
53ms |
Stylesheet
text/css |
2a00:1450:4001:c1f::5f Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
jquery-3.2.1.slim.min.js
Show response
code.jquery.com/ |
68 KB 24 KB |
35ms
7ms |
Script
application/javascript |
2a04:4e42::411 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
bootstrap.min.js
Show response
maxcdn.bootstrapcdn.com/bootstrap/4.0.0/js/ |
48 KB 14 KB |
37ms
23ms |
Script
application/javascript |
104.18.10.207 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
us.js
antivirus.my.id/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
picasa.jpg
data-recovery.wiki/wp-content/uploads/2022/05/ |
186 KB 185 KB |
636ms
312ms |
Image
image/webp |
23.81.204.137 Leaseweb USA |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 |
why-jpeg-image-cannot-open-in-photoshop.jpg
www.izitru.com/wp-content/uploads/2023/09/ |
135 KB 135 KB |
524ms
185ms |
Image
image/jpeg |
154.9.154.230 Charles River Ope... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
Picasa-765x249.png
appsforwin10.com/wp-content/uploads/2015/09/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
404 |
maxresdefault.jpg
i.ytimg.com/vi/QVNmyb5B9zo/ |
1 KB 1 KB |
142ms
54ms |
Image
image/jpeg |
2a00:1450:4001:c25::77 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
ce12b1c6c5d675861cf47eec44014ac6.png
i.pinimg.com/originals/ce/12/b1/ |
862 KB 863 KB |
247ms
223ms |
Image
image/png |
2a02:26f0:3500:12::1730:1793 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Picasa-logo-1024x1024.jpg
i0.wp.com/softonline.net/wp-content/uploads/2020/10/ |
19 KB 20 KB |
62ms
38ms |
Image
image/webp |
192.0.77.2 Automattic |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
persona-3-reload-release-date.jpg
www.pcgamesn.com/wp-content/sites/pcgamesn/2023/10/ |
276 KB 277 KB |
183ms
120ms |
Image
image/jpeg |
2606:4700:10::ac42:ad14 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
python-ne-ise-yarar.png
www.uzaktanegitim.com/images/blog/ |
59 KB 59 KB |
105ms
21ms |
Image
image/png |
168.119.121.23 HETZNER-AS Hetzne... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
comprar_casa-1068x587.jpg
hch.tv/wp-content/uploads/2019/07/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
maxresdefault.jpg
i.ytimg.com/vi/o2iOd3o-4kA/ |
86 KB 86 KB |
212ms
126ms |
Image
image/jpeg |
2a00:1450:4001:c25::77 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
picasa-benzeri-uygulamalar-1.jpg
img.tamindir.com/resize/1200x675/2022/12/476734/ |
43 KB 44 KB |
67ms
30ms |
Image
image/jpeg |
2606:4700:20::681a:4c7 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Aferin-Ne-Ise-Yarar-850x478.png
trendkiz.com/wp-content/uploads/2022/05/ |
138 KB 138 KB |
282ms
96ms |
Image
image/png |
185.126.218.147 VOYAR VOYAR VERIM... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
JFIF-Format-1-1-600x338.jpg
pocketranger.com/wp-content/uploads/2021/05/ |
19 KB 19 KB |
77ms
38ms |
Image
image/jpeg |
2606:4700:3037::ac43:867c Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
81feae5fcf828266c7d5746de9dd54a6.jpg
i.pinimg.com/originals/81/fe/ae/ |
10 KB 10 KB |
204ms
202ms |
Image
image/jpeg |
2a02:26f0:3500:12::1730:1793 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
b31c11da2fb426eec3533a47d42e0312.jpg
i.pinimg.com/originals/b3/1c/11/ |
37 KB 37 KB |
190ms
188ms |
Image
image/jpeg |
2a02:26f0:3500:12::1730:1793 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
maxresdefault.jpg
i.ytimg.com/vi/mIBAxTWtSwU/ |
101 KB 102 KB |
147ms
145ms |
Image
image/jpeg |
2a00:1450:4001:c25::77 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
ae74fa439561224219f6f7eaa15ff614.png
i.pinimg.com/originals/ae/74/fa/ |
398 KB 398 KB |
135ms
134ms |
Image
image/png |
2a02:26f0:3500:12::1730:1793 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Old_Photos_Archiving-980x551.jpg
peaceofmindtransitions.b-cdn.net/wp-content/uploads/2020/06/ |
177 KB 178 KB |
647ms
612ms |
Image
image/jpeg |
2400:52e0:1e00:2::1329:1 CDN77 Datacamp Li... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
ea522763-3aef-4266-a873-8dcf237db3ea.png
gdm-catalog-fmapi-prod.imgix.net/ProductScreenshot/ |
127 KB 127 KB |
384ms
338ms |
Image
image/avif |
2a04:4e42:200::720 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
l.jpg
s3-media4.ak.yelpcdn.com/bphoto/qolK-U4RTFqt6DHQnZSrpQ/ |
40 KB 41 KB |
209ms
156ms |
Image
image/jpeg |
151.101.193.91 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
PICC-1024x1024.jpg
neolifeclinica.com.br/wp-content/uploads/2022/10/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
CA-kya-hota-hai-hindi.jpg
freelatestjob.in/wp-content/uploads/2022/02/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
maxresdefault.jpg
i.ytimg.com/vi/xpPU8ZQvHuI/ |
70 KB 70 KB |
111ms
111ms |
Image
image/jpeg |
142.251.20.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
google-picasa.jpg
bramjnaa.com/wp-content/uploads/ |
71 KB 72 KB |
66ms
14ms |
Image
image/jpeg |
142.132.217.230 HETZNER-AS Hetzne... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Picasa.png
2.bp.blogspot.com/-6ezcpmSdrHI/UtO0B286oNI/AAAAAAAAAZQ/JxPncNcPxkgitycsCy4oh682cDZK3a-FACPcB/s1600/ |
697 KB 698 KB |
777ms
686ms |
Image
image/png |
2a00:1450:4001:c17::84 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
/
neurotechnologycloud.com/ Redirect Chain
|
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
Ventajas-y-desventajas.jpg
www.elerniam.com/wp-content/uploads/2016/12/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
88060Learn-Facial-Recognition-scaled.jpg
editor.analyticsvidhya.com/uploads/ |
490 KB 491 KB |
718ms
681ms |
Image
image/jpeg |
2606:4700:20::681a:c6d Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
picasa.jpg
blog.vilmatech.com/wp-content/uploads/2017/08/ |
71 KB 72 KB |
194ms
157ms |
Image
image/jpeg |
172.67.174.33 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
compress-jpeg-to-100kb.jpg
compressjpeg.online/assets/img/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
persona-1.jpg
assetsio.reedpopcdn.com/ |
103 KB 103 KB |
91ms
43ms |
Image
image/webp |
2a04:4e42:400::311 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
Picasa-Image-Editor-Free-Download.png
allpcworld.com/wp-content/uploads/2016/09/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
suspendedpage.cgi
romsx.com/cgi-sys/ Redirect Chain
|
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
d0411a3d2c792a89ce00852b12946a91.jpg
i.pinimg.com/originals/d0/41/1a/ |
40 KB 40 KB |
187ms
186ms |
Image
image/jpeg |
2a02:26f0:3500:12::1730:1793 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
Bellagio---Picasso---Patio-HiRes.jpg
media.cntraveler.com/photos/5a79b1aa81e0f7699049e000/16:9/w_2560%2Cc_limit/ |
372 KB 373 KB |
85ms
16ms |
Image
image/webp |
3.167.227.35 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
1801568_1.gif
img.informer.com/screenshots/1801/ Redirect Chain
|
37 KB 37 KB |
203ms
165ms |
Image
image/gif |
2606:4700:10::6814:11cb Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
Pilas-cilindricas.jpg
247tecno.com/wp-content/uploads/2018/05/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
maxresdefault.jpg
i.ytimg.com/vi/xvx8DY5Xuf4/ |
57 KB 57 KB |
113ms
113ms |
Image
image/jpeg |
142.251.20.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
404 |
th
tse2.mm.bing.net/ |
1 KB 1 KB |
92ms
37ms |
Image
image/jpeg |
2620:1ec:33::10 Microsoft Corpora... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
404 |
th
tse2.mm.bing.net/ |
1 KB 1 KB |
91ms
36ms |
Image
image/jpeg |
2620:1ec:33::10 Microsoft Corpora... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
th
tse2.mm.bing.net/ |
32 KB 33 KB |
82ms
27ms |
Image
image/jpeg |
2620:1ec:33::10 Microsoft Corpora... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
404 |
th
tse2.mm.bing.net/ |
1 KB 1 KB |
195ms
194ms |
Image
image/jpeg |
2620:1ec:33::10 Microsoft Corpora... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
404 |
th
tse2.mm.bing.net/ |
1 KB 1 KB |
417ms
417ms |
Image
image/jpeg |
2620:1ec:33::10 Microsoft Corpora... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
th
tse4.mm.bing.net/ |
17 KB 17 KB |
55ms
27ms |
Image
image/jpeg |
2620:1ec:33::10 Microsoft Corpora... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
th
tse1.mm.bing.net/ |
19 KB 19 KB |
40ms
29ms |
Image
image/jpeg |
2620:1ec:33::10 Microsoft Corpora... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
th
tse3.mm.bing.net/ |
16 KB 16 KB |
57ms
27ms |
Image
image/jpeg |
2620:1ec:33::10 Microsoft Corpora... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
404 |
th
tse4.mm.bing.net/ |
1 KB 1 KB |
39ms
39ms |
Image
image/jpeg |
2620:1ec:33::10 Microsoft Corpora... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
404 |
th
tse4.mm.bing.net/ |
1 KB 1 KB |
197ms
197ms |
Image
image/jpeg |
2620:1ec:33::10 Microsoft Corpora... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
favicon.ico
picasasupport.pages.dev/ |
30 KB 7 KB |
38ms
38ms |
Other
text/html |
188.114.97.3 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||


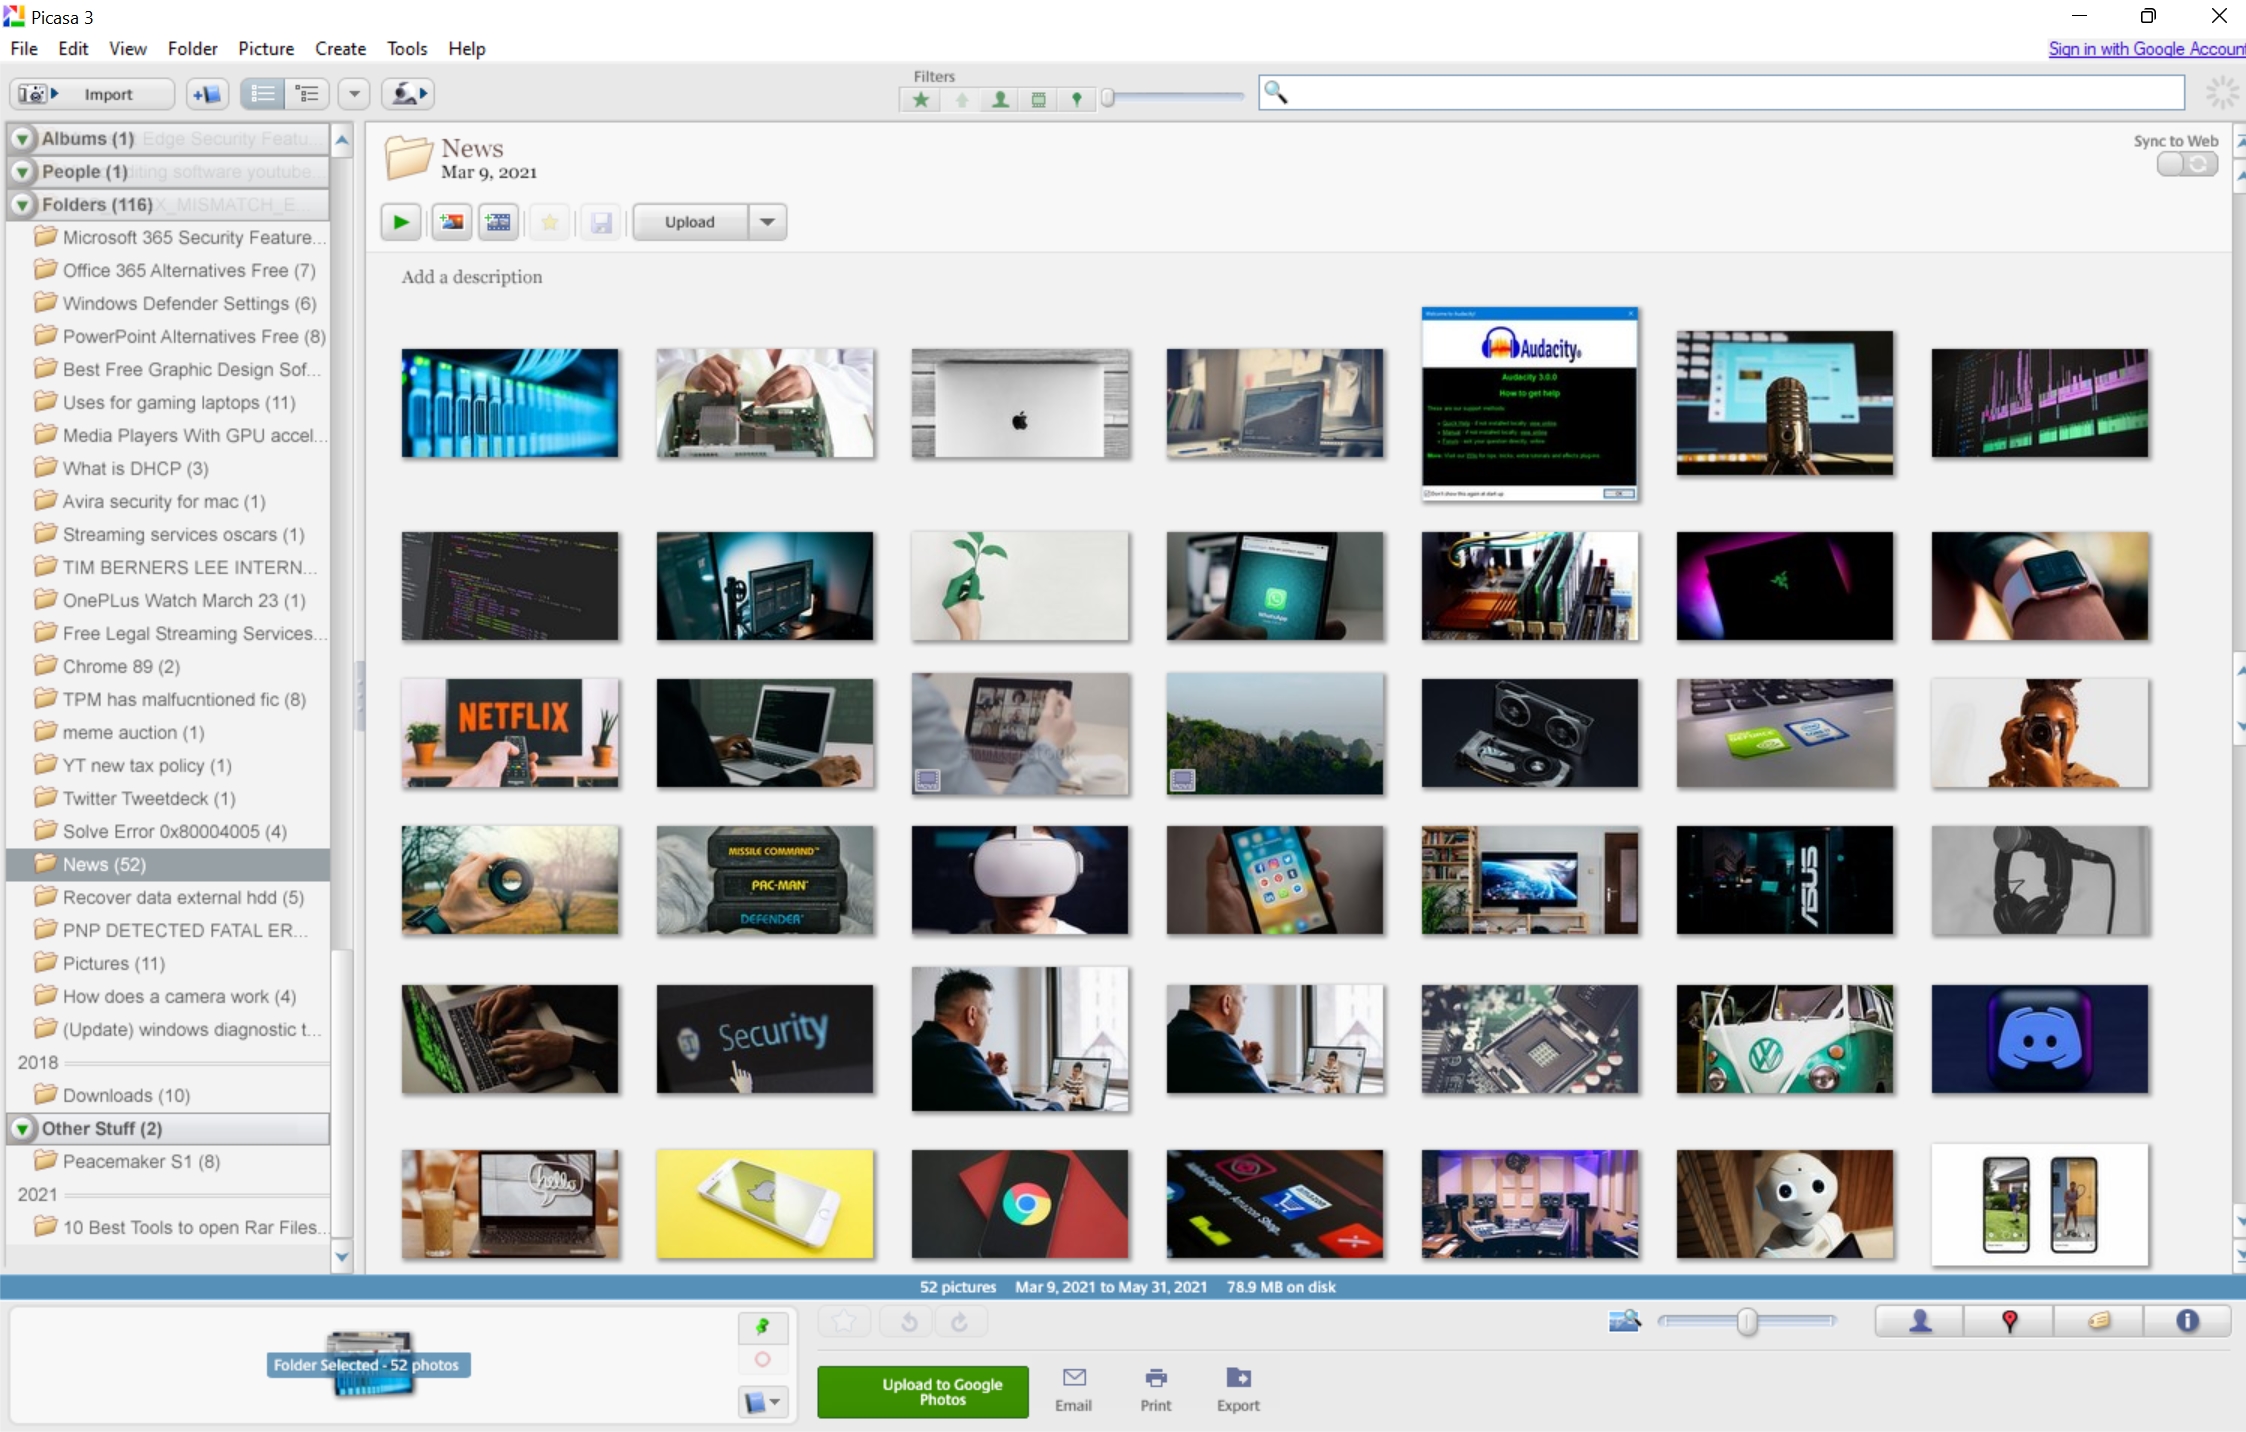





























Failed requests
These URLs were requested, but there was no response received. You will also see them in the list above.
- Domain
- antivirus.my.id
- URL
- https://antivirus.my.id/us.js
- Domain
- appsforwin10.com
- URL
- https://appsforwin10.com/wp-content/uploads/2015/09/Picasa-765x249.png
- Domain
- hch.tv
- URL
- https://hch.tv/wp-content/uploads/2019/07/comprar_casa-1068x587.jpg
- Domain
- neolifeclinica.com.br
- URL
- https://neolifeclinica.com.br/wp-content/uploads/2022/10/PICC-1024x1024.jpg
- Domain
- freelatestjob.in
- URL
- https://freelatestjob.in/wp-content/uploads/2022/02/CA-kya-hota-hai-hindi.jpg
- Domain
- neurotechnologycloud.com
- URL
- https://neurotechnologycloud.com/
- Domain
- www.elerniam.com
- URL
- https://www.elerniam.com/wp-content/uploads/2016/12/Ventajas-y-desventajas.jpg
- Domain
- compressjpeg.online
- URL
- https://compressjpeg.online/assets/img/compress-jpeg-to-100kb.jpg
- Domain
- allpcworld.com
- URL
- https://allpcworld.com/wp-content/uploads/2016/09/Picasa-Image-Editor-Free-Download.png
- Domain
- romsx.com
- URL
- https://romsx.com/cgi-sys/suspendedpage.cgi
- Domain
- 247tecno.com
- URL
- https://247tecno.com/wp-content/uploads/2018/05/Pilas-cilindricas.jpg
Verdicts & Comments Add Verdict or Comment
3 JavaScript Window variables
Go Pro
Only in urlscan Pro
Inspect and pivot on JavaScript variables, identifiers, and other key site metadata data with urlscan Pro. Reveal and search on client-side frameworks, runtime variables, and custom values.
Click for more information
Free trials of urlscan Pro are available.
These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.
function| $ function| jQuery object| bootstrap0 Cookies
Go Pro
Only in urlscan Pro
Review, search, and pivot on browser cookies and persistence site data to see how a site tracks users and keeps sessions alive across visits.
Click for more information
Free trials of urlscan Pro are available.
Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.
18 Console Messages
A page may trigger messages to the console to be logged. These are often error messages about being unable to load a resource or execute a piece of JavaScript. Sometimes they also provide insight into the technology behind a website.
| Source | Level | URL Text |
|---|
Security Headers
This page lists any security headers set by the main page. If you want to understand what these mean and how to use them, head on over to this page
| Header | Value |
|---|---|
| X-Content-Type-Options | nosniff |
Indicators
This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.
2.bp.blogspot.com
247tecno.com
allpcworld.com
antivirus.my.id
appsforwin10.com
assetsio.reedpopcdn.com
blog.vilmatech.com
bramjnaa.com
code.jquery.com
compressjpeg.online
data-recovery.wiki
editor.analyticsvidhya.com
fonts.googleapis.com
freelatestjob.in
gdm-catalog-fmapi-prod.imgix.net
hch.tv
i.pinimg.com
i.ytimg.com
i0.wp.com
img.informer.com
img.tamindir.com
maxcdn.bootstrapcdn.com
media.cntraveler.com
neolifeclinica.com.br
neurotechnologycloud.com
peaceofmindtransitions.b-cdn.net
picasasupport.pages.dev
pocketranger.com
romsx.com
s.getwinpcsoft.com
s3-media4.ak.yelpcdn.com
stackpath.bootstrapcdn.com
trendkiz.com
tse1.mm.bing.net
tse2.mm.bing.net
tse3.mm.bing.net
tse4.mm.bing.net
www.elerniam.com
www.izitru.com
www.pcgamesn.com
www.uzaktanegitim.com
247tecno.com
allpcworld.com
antivirus.my.id
appsforwin10.com
compressjpeg.online
freelatestjob.in
hch.tv
neolifeclinica.com.br
neurotechnologycloud.com
romsx.com
www.elerniam.com
104.18.10.207
142.132.217.230
142.251.20.119
151.101.193.91
154.9.154.230
168.119.121.23
172.67.174.33
185.126.218.147
188.114.97.3
192.0.77.2
198.58.126.96
23.81.204.137
2400:52e0:1e00:2::1329:1
2606:4700:10::6814:11cb
2606:4700:10::ac42:ad14
2606:4700:20::681a:4c7
2606:4700:20::681a:c6d
2606:4700:3037::ac43:867c
2620:1ec:33::10
2a00:1450:4001:c17::84
2a00:1450:4001:c1f::5f
2a00:1450:4001:c25::77
2a02:26f0:3500:12::1730:1793
2a04:4e42:200::720
2a04:4e42:400::311
2a04:4e42::411
3.167.227.35
038f0e2f6ba16959ed13090b11654b82c5e8329a8528887e0f3d2f1c772ab43c
04a9f0a25488e6aebffd583a5948a1729dc5d41cbfa82e383173a9fdecc01050
060ba33be537656f8150df220918a3bd02c068eb8a0a83b7d60d176b7c452534
069f34cce479953267b034fc73e314bb2674f82c537a1dfce1f950ac2eff7882
20e9aab22032d85684d7d916a1013f7c577a132a5b10ea3fd3578e8d0b28a711
24920bfa6ff1ccd63ef09a155c8b7fb15055385e3143e7719754d37b4941a52d
25c8ac81468ec9afbfc07ec6ada43272bf671574e91ee830b0acd21b96648abb
36cbc8edf63260b8b3d9a827aee5ac721de768306c5231e22498de2c1232d358
3e8d1fb192164870c0fbc30938a118300503fc9c35f01a2931087168439de484
3fea22be2c88470e0e113cb83de88d2c986ab9546de7341152df52d1c1b1ee67
475dc08f0022013ce5827de3372d6d179d4b1c65f5cb33e5d2d8bb2c0334e261
4d79cb81807ec0117e4f7e5e9d56da6a0338a87d258090159668f7d5c7f76c55
4ff517934bdf0cbec647faf785f504c6f130298f255e8b89942ff9d07f83aa3e
5f8d6e5f1c852f00571b551047a8bf370bd994233e7dcafd91a5f740e51c2295
68ff8b44c2396789b4ab9c990e522b6610d680c8209da7cb51c6df50ef433093
7928b5ab63c6e89ee0ee26f5ef201a58c72baf91abb688580a1aa26eb57b3c11
85661f26a69f2fd5831853dc215b4c0e743112072c268b283766f78ee9a62748
8b8eb7c2bf7634a1d989ba7e838e1c3a4628bea7f68f49760a52c8c746afad38
92b0f847d39b39419d8885eae6edf01d817639e9c44ebbd2ff2ef7d85b315a2f
9365920887b11b33a3dc4ba28a0f93951f200341263e3b9cefd384798e4be398
9466256f233961416197414d46901947b20a4d631728d7b134581799b7d84386
9a694425567feda2b28363f182d29a4e0eaabdd929b2a83d602d8f738a189a8f
9f92e1065e36c40eff7af85487f32971e161c13decada8216d8e03d36ab43b17
a01fe8e8ba81fbda0658151bc84b83bfbfe4d19c6bbc61d4237973b2f5a5e6aa
a4e54e23416785c28bd4ef6f1536425e676e4b2f0ee55aa85a0a6039806bee5d
a727fd77460720d813278c73b99622e15d7bb1b97b249f7dc9a6804a9b177169
ba74acd4eeb9a04f60c46b1d7cecc10403a7a93c3ecb78a8cb73621b07bf1b2d
bdfc6c55b50cae29c710a723218c01dd8d887518c16e970664d511177744b6ea
caf680d3c767a64e43283269da378441167beffe2b76704cc1188d00208f6676
d16ab6e5e4a03cdfbcf7fbf573859de77ae55848f4ac93c443f981ce8cda7aa6
d90444a4fad0d520529f458bedf559b17c8b4fc7a2c5780cf553938697dd06bd
e7ed36ceee5450b4243bbc35188afabdfb4280c7c57597001de0ed167299b01b
edb0e61acd1775a5eea4dd920bc0c1991d3576c8ed859c6dfb878fe86d4a2912
eea117bb5298b979142f4a7fdfe17a0190c5230b7201e4a601dd955ef20c5b95
fa6a1c462af13df195eb3d7ee2db7274cd3c2671f3a43f73ec027ef10d2a172d
fccafbb32a130accf66d96c156d8c5f00f5f3a52b3988b0e3d8d7799bb109610
ffc8b4720dea409c6ce3ea73691e3a61af7651fbc615b50752c50ca9c3abbd46