
musclegol.netlify.app
63.176.8.218
Public Scan
Open in
urlscan Pro
http://musclegol.netlify.app/ 2yr old
Effective URL:
https://musclegol.netlify.app/ 2yr old
Submission: On August 29 via api (August 29th 2026, 3:51:31 pm UTC) from US — Scanned from IL Go Pro
Only in urlscan Pro
- Select different country locations for Private Scans.
- Use a global network of additional scanning locations and residential IPs for scanning.
- Interact with pages while you are scanning them.
- Download files from remote websites.
- Scan websites on the Tor Network.
Summary
TLS certificate: Issued by DigiCert Global G2 TLS RSA SHA256 202... on February 16th 2026. Valid for: 1yr.
This is the only time musclegol.netlify.app was scanned on urlscan.io!
urlscan.io Verdict: No classification
Domain & IP information
| IP Address | AS Autonomous System | ||
|---|---|---|---|
| 3 | 63.176.8.218 63.176.8.218 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 1 | 104.26.2.230 104.26.2.230 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 104.16.78.6 104.16.78.6 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 172.66.145.102 172.66.145.102 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 192.0.66.223 192.0.66.223 | 2635 (AUTOMATTIC) (AUTOMATTIC - Automattic) | |
| 1 | 52.216.207.83 52.216.207.83 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 1 | 65.9.130.79 65.9.130.79 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 1 | 129.43.254.99 129.43.254.99 | 6150 (NCIFCRF) (NCIFCRF - National Cancer Institute) | |
| 1 | 142.250.154.119 142.250.154.119 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 104.20.0.51 104.20.0.51 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 18 | 11 |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: ec2-63-176-8-218.eu-central-1.compute.amazonaws.com
| musclegol.netlify.app 2yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| static.macupdate.com 7yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| res.cloudinary.com 10yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| mac-cdn.softpedia.com 8yr old |
ASN2635 (AUTOMATTIC - Automattic, Inc, US)
| www.dailydot.com 10yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: s3-1-w.amazonaws.com
| mightydeals.s3.amazonaws.com 9yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-65-9-130-79.fra60.r.cloudfront.net
| images-wixmp-ed30a86b8c4ca887773594c2.wixmp.com 8yr old |
ASN6150 (NCIFCRF - National Cancer Institute, US)
| brb.nci.nih.gov 6yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: bt-in-f119.1e100.net
| i.ytimg.com 10yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| static.filehorse.com 9yr old |
| Apex Domain Subdomains |
Transfer | |
|---|---|---|
| 3 |
netlify.app
musclegol.netlify.app 2yr old |
53 KB |
| 1 |
filehorse.com
static.filehorse.com 9yr old |
159 KB |
| 1 |
ytimg.com
i.ytimg.com — Cisco Umbrella Rank: 126 10yr old |
60 KB |
| 1 |
nih.gov
brb.nci.nih.gov 6yr old |
220 KB |
| 1 |
wixmp.com
images-wixmp-ed30a86b8c4ca887773594c2.wixmp.com — Cisco Umbrella Rank: 36339 8yr old |
234 KB |
| 1 |
amazonaws.com
mightydeals.s3.amazonaws.com 9yr old |
84 KB |
| 1 |
dailydot.com
www.dailydot.com 10yr old |
188 B |
| 1 |
softpedia.com
mac-cdn.softpedia.com 8yr old |
79 KB |
| 1 |
cloudinary.com
res.cloudinary.com — Cisco Umbrella Rank: 3813 10yr old |
55 KB |
| 1 |
macupdate.com
static.macupdate.com 7yr old |
95 KB |
| 0 |
canon.com
Failed
support.usa.canon.com Failed 11yr old |
|
| 0 |
unstoppable.ai
Failed
unstoppable.ai Failed 6yr old |
|
| 0 |
isu.pub
Failed
image.isu.pub Failed 10yr old |
|
| 0 |
levelgeek.net
Failed
levelgeek.net Failed 9yr old |
|
| 0 |
cbsistatic.com
Failed
dl1.cbsistatic.com Failed 10yr old |
|
| 18 | 15 |
| Domain | Requested by | |
|---|---|---|
| 3 | musclegol.netlify.app |
musclegol.netlify.app
|
| 1 | static.filehorse.com |
musclegol.netlify.app
|
| 1 | i.ytimg.com |
musclegol.netlify.app
|
| 1 | brb.nci.nih.gov |
musclegol.netlify.app
|
| 1 | images-wixmp-ed30a86b8c4ca887773594c2.wixmp.com |
musclegol.netlify.app
|
| 1 | mightydeals.s3.amazonaws.com |
musclegol.netlify.app
|
| 1 | www.dailydot.com |
musclegol.netlify.app
|
| 1 | mac-cdn.softpedia.com |
musclegol.netlify.app
|
| 1 | res.cloudinary.com |
musclegol.netlify.app
|
| 1 | static.macupdate.com |
musclegol.netlify.app
|
| 0 | support.usa.canon.com Failed |
musclegol.netlify.app
|
| 0 | unstoppable.ai Failed |
musclegol.netlify.app
|
| 0 | image.isu.pub Failed |
musclegol.netlify.app
|
| 0 | levelgeek.net Failed |
musclegol.netlify.app
|
| 0 | dl1.cbsistatic.com Failed |
musclegol.netlify.app
|
| 18 | 15 |
This site contains no links.
| Subject Issuer | Validity | Valid | |
|---|---|---|---|
| *.netlify.app DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2026-02-16 - 2027-03-19 |
1yr | crt.sh |
| 87aa2575.sni.cloudflaressl.com WE1 |
2026-07-20 - 2026-10-18 |
3mo | crt.sh |
| *.cloudinary.com Go Daddy Secure Certificate Authority - G2 |
2026-05-18 - 2026-12-02 |
7mo | crt.sh |
| softpedia.com Sectigo Public Server Authentication CA DV R36 |
2026-05-07 - 2026-11-21 |
7mo | crt.sh |
| dailydot.com YE1 |
2026-07-20 - 2026-10-18 |
3mo | crt.sh |
| s3.amazonaws.com Amazon RSA 2048 M04 |
2025-11-18 - 2026-11-06 |
1yr | crt.sh |
| *.wixmp.com YR2 |
2026-08-05 - 2026-11-03 |
3mo | crt.sh |
| *.nci.nih.gov DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2026-08-24 - 2027-03-10 |
7mo | crt.sh |
| edgestatic.com WR2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| filehorse.com WE1 |
2026-08-12 - 2026-11-10 |
3mo | crt.sh |
This page contains 1 frames:
Primary Page:
https://musclegol.netlify.app/
Frame ID: 8E36D36C9F327E6AA64CFB299E91B843
Requests: 18 HTTP requests in this frame
Screenshot
Go Pro
Only in urlscan Pro
Use the Visual Search feature to find pages with visually similar screenshots.
Click for more information
Free trials of urlscan Pro are available.
Page Title
MusclegolPage URL History
Go Pro
Only in urlscan Pro
Search our real-time database of newly observed domains and
hostnames. Pivot on different attributes, and setup keyword alerts for
newly observed domains.
Click for more information
Free trials of urlscan Pro are available.
Show full URLs
-
http://musclegol.netlify.app/
HTTP 307
https://musclegol.netlify.app/ Page URL
Detected technologies
 WordPress
(CMS)
Expand
Detected patterns
- /wp-(?:content|includes)/
 Netlify
(PaaS)
Expand
Detected patterns
- ^https?://[^/]+\.netlify\.(?:com|app)/
 Amazon S3
(CDN)
Expand
Detected patterns
- s3[^ ]*\.amazonaws\.com/
Page Statistics
0 Outgoing links
Go Pro
Only in urlscan Pro
Effortlessly use any on-page link as a pivot to discover other pages pointing to the exact same destination. Seamlessly trace both specific URLs and broader domains to uncover hidden connection networks and map out backlink relationships with ease.
Click for more information
Free trials of urlscan Pro are available.
These are links going to different origins than the main page.
Page URL History
This captures the URL locations of the websites, including HTTP redirects and client-side redirects via JavaScript or Meta fields.
-
http://musclegol.netlify.app/
HTTP 307
https://musclegol.netlify.app/ Page URL
Redirected requests
There were HTTP redirect chains for the following requests:
Request Chain 14- https://www.gamechains.com/wp-content/uploads/2016/06/download-Yu-Gi-Oh-Duel-Generation-free-apk.jpg HTTP 302
- https://unstoppabledomains.com/d/gamechains.com HTTP 302
- https://unstoppable.ai/d/gamechains.com
18 HTTP transactions
Go Pro
Only in urlscan Pro
Inspect WebSocket connections, examine POST data effortlessly, and track overlap counts in real time. Features live search and filtering across all HTTP output, complete with full response metadata for deep analysis.
Click for more information
Free trials of urlscan Pro are available.
0 data transactions
| Method Protocol |
Status | Resource Path |
Size x-fer |
Time Latency |
Type MIME-Type |
IP Location |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
|
GET H2 |
200 |
Primary Request
/
Show response
musclegol.netlify.app/ Redirect Chain
|
24 KB 6 KB |
846ms
602ms |
Document
text/html |
63.176.8.218 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
style.css
musclegol.netlify.app/ |
142 KB 47 KB |
229ms
229ms |
Stylesheet
text/css |
63.176.8.218 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
xcode-screenshot.png
static.macupdate.com/screenshots/251570/m/ |
95 KB 95 KB |
564ms
418ms |
Image
image/png |
104.26.2.230 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
imgingest-5819537534905576664.png
dl1.cbsistatic.com/i/2018/01/11/93a11960-03d4-451a-a0ba-e9fd6d150d67/2415d87d6663dab24b3122f9b7f52ab5/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
bdheader-49457.png
res.cloudinary.com/lmn/image/upload/e_sharpen:100/f_auto,fl_lossy,q_auto/v1/gameskinnyc/b/d/h/ |
54 KB 55 KB |
796ms
626ms |
Image
image/webp |
104.16.78.6 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Sonos-Desktop-Controller_5.jpg
mac-cdn.softpedia.com/screenshots/ |
79 KB 79 KB |
434ms
236ms |
Image
image/jpeg |
172.66.145.102 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
404 |
1be82c0a5d03a8a20b745907d917c298.jpg
www.dailydot.com/wp-content/uploads/96b/38/ |
0 188 B |
401ms
143ms |
Image
text/html |
192.0.66.223 Automattic |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
5.png
mightydeals.s3.amazonaws.com/images/boho-family/ |
84 KB 84 KB |
752ms
306ms |
Image
image/png |
52.216.207.83 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
ESCAPE-FROM-TARKOV-NEW-HACK-EFT-HACK-ESCAPE-FROM-TARKOV.jpg
levelgeek.net/wp-content/uploads/2020/03/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
d4cepwj-2ba96346-51d3-47b2-b866-9589889566da.jpg
images-wixmp-ed30a86b8c4ca887773594c2.wixmp.com/i/239b653d-f365-41d5-be1c-a100fc85e203/ |
233 KB 234 KB |
703ms
431ms |
Image
image/jpeg |
65.9.130.79 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
image001.png
brb.nci.nih.gov/seqtools/images/ubuntu/ |
219 KB 220 KB |
2821ms
266ms |
Image
image/png |
129.43.254.99 National Cancer I... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
maxresdefault.jpg
i.ytimg.com/vi/tnKh5kcT4Y0/ |
60 KB 60 KB |
455ms
204ms |
Image
image/jpeg |
142.250.154.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
fmimg503640185479315324.jpg
dl1.cbsistatic.com/i/r/2017/02/01/c5787cf8-1fdb-4f2c-82a9-9cb0cbf48d12/resize/257xauto/29b44cf26111c7d81bc11c3736c80f2f/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
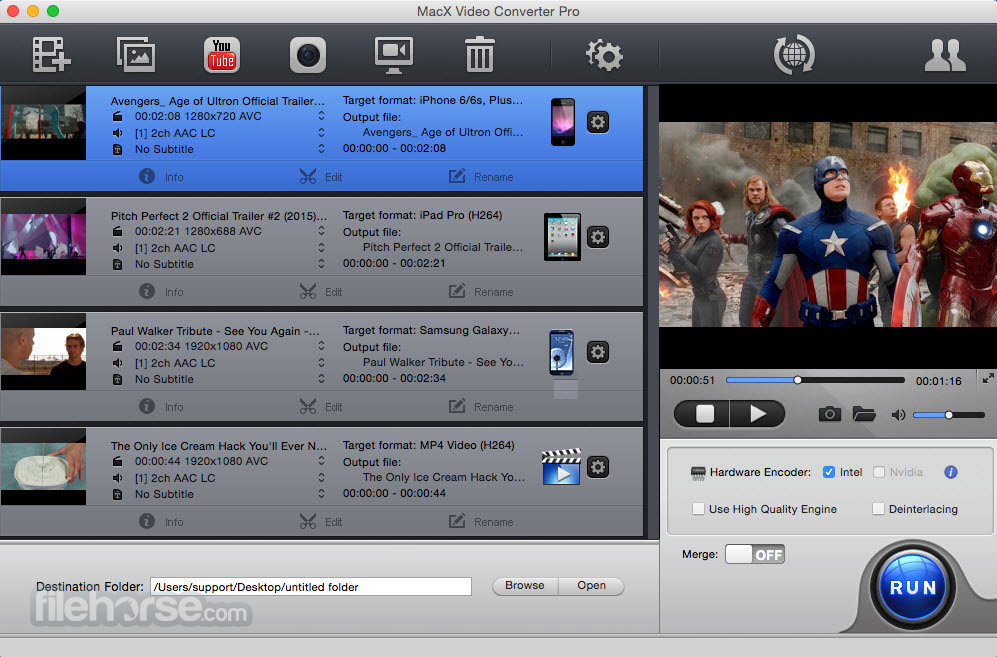
macx-video-converter-pro-screenshot-01.jpg
static.filehorse.com/screenshots-mac/video-software/ |
159 KB 159 KB |
263ms
162ms |
Image
image/jpeg |
104.20.0.51 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
page_1.jpg
image.isu.pub/170523060138-d4fc663ee0abedbeb448062ce3f972a0/jpg/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
gamechains.com
unstoppable.ai/d/ Redirect Chain
|
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
mp502.gif
support.usa.canon.com/library/attachments/ServiceWareImages/LDImages/SolutionAnswer/MX870/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
favicon.ico
musclegol.netlify.app/ |
1 KB 644 B |
310ms
310ms |
Other
image/vnd.microsoft.icon |
63.176.8.218 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
















Failed requests
These URLs were requested, but there was no response received. You will also see them in the list above.
- Domain
- dl1.cbsistatic.com
- URL
- https://dl1.cbsistatic.com/i/2018/01/11/93a11960-03d4-451a-a0ba-e9fd6d150d67/2415d87d6663dab24b3122f9b7f52ab5/imgingest-5819537534905576664.png
- Domain
- levelgeek.net
- URL
- https://levelgeek.net/wp-content/uploads/2020/03/ESCAPE-FROM-TARKOV-NEW-HACK-EFT-HACK-ESCAPE-FROM-TARKOV.jpg
- Domain
- dl1.cbsistatic.com
- URL
- https://dl1.cbsistatic.com/i/r/2017/02/01/c5787cf8-1fdb-4f2c-82a9-9cb0cbf48d12/resize/257xauto/29b44cf26111c7d81bc11c3736c80f2f/fmimg503640185479315324.jpg
- Domain
- image.isu.pub
- URL
- https://image.isu.pub/170523060138-d4fc663ee0abedbeb448062ce3f972a0/jpg/page_1.jpg
- Domain
- unstoppable.ai
- URL
- https://unstoppable.ai/d/gamechains.com
- Domain
- support.usa.canon.com
- URL
- https://support.usa.canon.com/library/attachments/ServiceWareImages/LDImages/SolutionAnswer/MX870/mp502.gif
Verdicts & Comments Add Verdict or Comment
0 JavaScript Window variables
Go Pro
Only in urlscan Pro
Inspect and pivot on JavaScript variables, identifiers, and other key site metadata data with urlscan Pro. Reveal and search on client-side frameworks, runtime variables, and custom values.
Click for more information
Free trials of urlscan Pro are available.
These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.
0 Cookies
Go Pro
Only in urlscan Pro
Review, search, and pivot on browser cookies and persistence site data to see how a site tracks users and keeps sessions alive across visits.
Click for more information
Free trials of urlscan Pro are available.
Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.
3 Console Messages
A page may trigger messages to the console to be logged. These are often error messages about being unable to load a resource or execute a piece of JavaScript. Sometimes they also provide insight into the technology behind a website.
| Source | Level | URL Text |
|---|
Security Headers
This page lists any security headers set by the main page. If you want to understand what these mean and how to use them, head on over to this page
| Header | Value |
|---|---|
| Strict-Transport-Security | max-age=31536000; includeSubDomains; preload |
Indicators
This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.
brb.nci.nih.gov
dl1.cbsistatic.com
i.ytimg.com
image.isu.pub
images-wixmp-ed30a86b8c4ca887773594c2.wixmp.com
levelgeek.net
mac-cdn.softpedia.com
mightydeals.s3.amazonaws.com
musclegol.netlify.app
res.cloudinary.com
static.filehorse.com
static.macupdate.com
support.usa.canon.com
unstoppable.ai
www.dailydot.com
dl1.cbsistatic.com
image.isu.pub
levelgeek.net
support.usa.canon.com
unstoppable.ai
104.16.78.6
104.20.0.51
104.26.2.230
129.43.254.99
142.250.154.119
172.66.145.102
192.0.66.223
52.216.207.83
63.176.8.218
65.9.130.79
062bccbf4598de9f951674ab18a377abaabaa805e55133a474299bfd490d12dc
0ab9ea3828aef04155f2277cbae8e8e5624875ba849e5d1295894653d8b676fc
1a4ad252beb2a4af0d316d4b778944934184182accba9699f0c650821a2eb890
1d13cd2db38d2ce5680d1271259e3254a5f14335dc9f398a8f467a7c2c9ebe5a
44e8c95b20cf5452be834c32960980ae19f3029e55e8139e095863fd3156fd6d
4a33d27f93b631f9a882cb958500bee777fb773f12773df6d26e2b5acd63d5f3
5a193ed9cab24596bcfc18ac020d70ebee36a570576dee34aa2ad8084cbb8bae
b5ad468a9ac291f74267cda5c25a36524b156f9b79ef4e4d9ac0952f7bea05c6
c2e67d8dae030392107208656137be4b28cbb1b1bebc8cc88a2096518b17e7a1
d5291c69a872c37c8e6e175f9bb5d5c607ab212cc0eeaa2f9b6ad10a0eff2b7c
e267ec8a33e2de582f252684ec8888c3bceea20081353f3dc07621227d75f5ab
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855