termsandconditions-5wn.pages.dev
188.114.96.3  Public Scan Open in urlscan Pro

Summary

This website contacted 16 IPs in 4 countries across 13 domains to perform 52 HTTP transactions. The main IP is 188.114.96.3, located in Ascension Island and belongs to CLOUDFLARENET - Cloudflare, Inc., US. The main domain is termsandconditions-5wn.pages.dev. 1yr old
TLS certificate: Issued by WE1 on August 13th 2026. Valid for: 3mo.
This is the only time termsandconditions-5wn.pages.dev was scanned on urlscan.io!

Domain & IP information

IP Address AS Autonomous System
1 188.114.96.3 188.114.96.3 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
1 172.64.146.183 172.64.146.183 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
12 65.8.131.2 65.8.131.2 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
5 150.171.27.10 150.171.27.10 8075 (MICROSOFT...) (MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation)
2 3.9.176.51 3.9.176.51 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
3 151.101.193.137 151.101.193.137 54113 (FASTLY) (FASTLY - Fastly)
1 151.101.192.84 151.101.192.84 54113 (FASTLY) (FASTLY - Fastly)
1 104.81.4.96 104.81.4.96 16625 (AKAMAI-AS) (AKAMAI-AS - Akamai Technologies)
6 142.251.20.97 142.251.20.97 15169 (GOOGLE) (GOOGLE - Google LLC)
1 23.215.20.211 23.215.20.211 16625 (AKAMAI-AS) (AKAMAI-AS - Akamai Technologies)
5 142.251.20.157 142.251.20.157 15169 (GOOGLE) (GOOGLE - Google LLC)
5 142.251.157.119 142.251.157.119 15169 (GOOGLE) (GOOGLE - Google LLC)
5 142.251.151.119 142.251.151.119 15169 (GOOGLE) (GOOGLE - Google LLC)
1 142.251.13.149 142.251.13.149 15169 (GOOGLE) (GOOGLE - Google LLC)
2 216.239.32.36 216.239.32.36 15169 (GOOGLE) (GOOGLE - Google LLC)
52 16
Apex Domain
Subdomains
Transfer
12 envato-static.com
public-assets.envato-static.com — Cisco Umbrella Rank: 75829 10yr old
178 KB
10 google.com
www.google.com — Cisco Umbrella Rank: 3 14yr old
4 KB
6 doubleclick.net
td.doubleclick.net — Cisco Umbrella Rank: 20982 4yr old
ad.doubleclick.net — Cisco Umbrella Rank: 132 10yr old
8 KB
6 googletagmanager.com
www.googletagmanager.com — Cisco Umbrella Rank: 52 14yr old
893 KB
5 bing.com
bat.bing.com — Cisco Umbrella Rank: 416 13yr old
16 KB
3 cloudinary.com
res.cloudinary.com — Cisco Umbrella Rank: 3813 10yr old
567 B
2 google-analytics.com
region1.google-analytics.com — Cisco Umbrella Rank: 4192 5yr old
2 cookiebot.com
imgsct.cookiebot.com — Cisco Umbrella Rank: 135368 4yr old
consentcdn.cookiebot.com — Cisco Umbrella Rank: 3965 8yr old
2 KB
2 lzd-cdn.org
g.lzd-cdn.org 1yr old
3 KB
1 pinimg.com
i.pinimg.com — Cisco Umbrella Rank: 2184 10yr old
74 KB
1 envatousercontent.com
market-resized.envatousercontent.com — Cisco Umbrella Rank: 85663 2yr old
71 KB
1 pages.dev
termsandconditions-5wn.pages.dev 1yr old
23 KB
0 wptheme.cloud Failed
wptheme.cloud Failed 6yr old
52 13
Domain Requested by
12 public-assets.envato-static.com termsandconditions-5wn.pages.dev
public-assets.envato-static.com
10 www.google.com td.doubleclick.net
www.googletagmanager.com
6 www.googletagmanager.com termsandconditions-5wn.pages.dev
www.googletagmanager.com
5 td.doubleclick.net termsandconditions-5wn.pages.dev
5 bat.bing.com termsandconditions-5wn.pages.dev
www.googletagmanager.com
bat.bing.com
3 res.cloudinary.com termsandconditions-5wn.pages.dev
2 region1.google-analytics.com www.googletagmanager.com
2 g.lzd-cdn.org termsandconditions-5wn.pages.dev
g.lzd-cdn.org
1 ad.doubleclick.net www.googletagmanager.com
1 consentcdn.cookiebot.com termsandconditions-5wn.pages.dev
1 imgsct.cookiebot.com termsandconditions-5wn.pages.dev
1 i.pinimg.com termsandconditions-5wn.pages.dev
1 market-resized.envatousercontent.com termsandconditions-5wn.pages.dev
1 termsandconditions-5wn.pages.dev
0 wptheme.cloud Failed termsandconditions-5wn.pages.dev
52 15
Subject Issuer Validity Valid
termsandconditions-5wn.pages.dev
WE1
2026-08-13 -
2026-11-11
3mo crt.sh
market-resized.envatousercontent.com
WE1
2026-08-11 -
2026-11-09
3mo crt.sh
public-assets.envato-static.com
Amazon RSA 2048 M01
2026-04-20 -
2026-11-03
7mo crt.sh
www.bing.com
Microsoft TLS G2 RSA CA OCSP 02
2026-08-28 -
2027-02-24
6mo crt.sh
*.lzd-cdn.org
YR1
2026-07-20 -
2026-10-18
3mo crt.sh
*.cloudinary.com
GlobalSign Atlas R3 DV TLS CA 2025 Q3
2025-09-23 -
2026-10-25
1yr crt.sh
*.pinterest.com
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2026-08-13 -
2027-02-26
7mo crt.sh
*.cookiebot.com
DigiCert Global G3 TLS ECC SHA384 2020 CA1
2025-11-10 -
2026-11-11
1yr crt.sh
*.google-analytics.com
WE2
2026-08-10 -
2026-11-02
3mo crt.sh
*.doubleclick.net
WE2
2026-08-10 -
2026-11-02
3mo crt.sh
www.google.com
WR2
2026-08-10 -
2026-11-02
3mo crt.sh

This page contains 7 frames:

Primary Page: https://termsandconditions-5wn.pages.dev/
Frame ID: 5E78E5F237BD90C38383A1A30EC94707
Requests: 41 HTTP requests in this frame

Frame: https://consentcdn.cookiebot.com/sdk/bc-v4.min.html
Frame ID: CBBDC915E4EEA7DDA16AC7ABFC1CAD72
Requests: 1 HTTP requests in this frame

Frame: https://td.doubleclick.net/td/rul/953691586?random=1753876666537&cv=11&fst=1753876666537&fmt=3&bg=ffffff&guid=ON&async=1&en=gtag.config&gtm=45be57s1z89195929391za200zb9195929391zd9195929391&gcd=13n3n3n3n5l1&dma=0&tag_exp=101509157~103116026~103200004~103233427~104684208~104684211~104948813~105103161~105103163~105124543~105124545&u_w=1920&u_h=1080&url=https%3A%2F%2Fthemeforest.net%2Fitem%2Fmarketica-marketplace-wordpress-theme%2F8988002%3Fsrsltid%3DAfmBOorwNEgJi-iQXu--3qzSatNlhXMhGjZ-gMFxbyMWP2LkJDdESL9b&ref=https%3A%2F%2Fwww.google.com%2F&hn=www.googleadservices.com&frm=0&tiba=Marketica%20-%20eCommerce%20and%20Marketplace%20-%20WooCommerce%20WordPress%20Theme%20by%20tokopress&npa=0&us_privacy=1---&pscdl=noapi&auid=786247872.1753876602&uaa=x86&uab=64&uafvl=Not)A%253BBrand%3B8.0.0.0%7CChromium%3B138.0.7204.183%7CGoogle%2520Chrome%3B138.0.7204.183&uamb=0&uam=&uap=Windows&uapv=19.0.0&uaw=0&fledge=1&data=event%3Dgtag.config
Frame ID: AFF52EF27CE4C6D8794EA6CC351AFA61
Requests: 2 HTTP requests in this frame

Frame: https://td.doubleclick.net/td/rul/943617023?random=1753876666603&cv=11&fst=1753876666603&fmt=3&bg=ffffff&guid=ON&async=1&en=gtag.config&gtm=45be57s1v889115050z89195929391za200zb9195929391zd9195929391&gcd=13n3n3n3n5l1&dma=0&tag_exp=101509157~103116026~103200004~103233427~104684208~104684211~104948813~105103161~105103163~105124543~105124545&u_w=1920&u_h=1080&url=https%3A%2F%2Fthemeforest.net%2Fitem%2Fmarketica-marketplace-wordpress-theme%2F8988002%3Fsrsltid%3DAfmBOorwNEgJi-iQXu--3qzSatNlhXMhGjZ-gMFxbyMWP2LkJDdESL9b&ref=https%3A%2F%2Fwww.google.com%2F&hn=www.googleadservices.com&frm=0&tiba=Marketica%20-%20eCommerce%20and%20Marketplace%20-%20WooCommerce%20WordPress%20Theme%20by%20tokopress&npa=0&us_privacy=1---&pscdl=noapi&auid=786247872.1753876602&uaa=x86&uab=64&uafvl=Not)A%253BBrand%3B8.0.0.0%7CChromium%3B138.0.7204.183%7CGoogle%2520Chrome%3B138.0.7204.183&uamb=0&uam=&uap=Windows&uapv=19.0.0&uaw=0&fledge=1&data=event%3Dgtag.config
Frame ID: C949DC47F343A1AD7675F297A2419AFD
Requests: 2 HTTP requests in this frame

Frame: https://td.doubleclick.net/td/rul/943617023?random=1753876666631&cv=11&fst=1753876666631&fmt=3&bg=ffffff&guid=ON&async=1&gtm=45be57s1v889115050z89195929391za200zb9195929391zd9195929391&gcd=13n3n3n3n5l1&dma=0&tag_exp=101509157~103116026~103200004~103233427~104684208~104684211~104948813~105103161~105103163~105124543~105124545&u_w=1920&u_h=1080&url=https%3A%2F%2Fthemeforest.net%2Fitem%2Fmarketica-marketplace-wordpress-theme%2F8988002%3Fsrsltid%3DAfmBOorwNEgJi-iQXu--3qzSatNlhXMhGjZ-gMFxbyMWP2LkJDdESL9b&ref=https%3A%2F%2Fwww.google.com%2F&hn=www.googleadservices.com&frm=0&tiba=Marketica%20-%20eCommerce%20and%20Marketplace%20-%20WooCommerce%20WordPress%20Theme%20by%20tokopress&did=dMWZhNz&gdid=dMWZhNz&npa=0&us_privacy=1---&pscdl=noapi&auid=786247872.1753876602&uaa=x86&uab=64&uafvl=Not)A%253BBrand%3B8.0.0.0%7CChromium%3B138.0.7204.183%7CGoogle%2520Chrome%3B138.0.7204.183&uamb=0&uam=&uap=Windows&uapv=19.0.0&uaw=0&fledge=1&_tu=Cg&data=ads_data_redaction%3Dfalse
Frame ID: 35EBFD58BCD6D07066B5B4046BCB0EE5
Requests: 2 HTTP requests in this frame

Frame: https://td.doubleclick.net/td/rul/800411572?random=1753876666684&cv=11&fst=1753876666684&fmt=3&bg=ffffff&guid=ON&async=1&en=gtag.config&gtm=45be57s1v896649154z89195929391za200zb9195929391zd9195929391&gcd=13n3n3n3n5l1&dma=0&tag_exp=101509157~103116026~103200004~103233427~104684208~104684211~104948813~105087538~105087540~105103161~105103163~105124543~105124545&u_w=1920&u_h=1080&url=https%3A%2F%2Fthemeforest.net%2Fitem%2Fmarketica-marketplace-wordpress-theme%2F8988002%3Fsrsltid%3DAfmBOorwNEgJi-iQXu--3qzSatNlhXMhGjZ-gMFxbyMWP2LkJDdESL9b&ref=https%3A%2F%2Fwww.google.com%2F&hn=www.googleadservices.com&frm=0&tiba=Marketica%20-%20eCommerce%20and%20Marketplace%20-%20WooCommerce%20WordPress%20Theme%20by%20tokopress&npa=0&us_privacy=1---&pscdl=noapi&auid=786247872.1753876602&uaa=x86&uab=64&uafvl=Not)A%253BBrand%3B8.0.0.0%7CChromium%3B138.0.7204.183%7CGoogle%2520Chrome%3B138.0.7204.183&uamb=0&uam=&uap=Windows&uapv=19.0.0&uaw=0&fledge=1&data=event%3Dgtag.config
Frame ID: A3CC375A75B73E0AC636DA382023DD75
Requests: 2 HTTP requests in this frame

Frame: https://td.doubleclick.net/td/rul/934741711?random=1753876666713&cv=11&fst=1753876666713&fmt=3&bg=ffffff&guid=ON&async=1&en=gtag.config&gtm=45be57s1v896649154z89195929391za200zb9195929391zd9195929391&gcd=13n3n3n3n5l1&dma=0&tag_exp=101509157~103116026~103200004~103233427~104684208~104684211~104948813~105087538~105087540~105103161~105103163~105124543~105124545&u_w=1920&u_h=1080&url=https%3A%2F%2Fthemeforest.net%2Fitem%2Fmarketica-marketplace-wordpress-theme%2F8988002%3Fsrsltid%3DAfmBOorwNEgJi-iQXu--3qzSatNlhXMhGjZ-gMFxbyMWP2LkJDdESL9b&ref=https%3A%2F%2Fwww.google.com%2F&hn=www.googleadservices.com&frm=0&tiba=Marketica%20-%20eCommerce%20and%20Marketplace%20-%20WooCommerce%20WordPress%20Theme%20by%20tokopress&npa=0&us_privacy=1---&pscdl=noapi&auid=786247872.1753876602&uaa=x86&uab=64&uafvl=Not)A%253BBrand%3B8.0.0.0%7CChromium%3B138.0.7204.183%7CGoogle%2520Chrome%3B138.0.7204.183&uamb=0&uam=&uap=Windows&uapv=19.0.0&uaw=0&fledge=1&data=event%3Dgtag.config
Frame ID: 51CDA93339D4946F5A89245001D4557B
Requests: 2 HTTP requests in this frame

Screenshot Go Pro

Only in urlscan Pro

Use the Visual Search feature to find pages with visually similar screenshots.
Click for more information
Free trials of urlscan Pro are available.

Page Title

KEBAYA4D : Situs Gacor Hujan Scatter Mudah Jackpot Maxwin

Detected technologies

(JavaScript frameworks)
Overall confidence: 100%
Detected patterns
  • <link rel="amphtml"

(Security)
Overall confidence: 100%
Detected patterns

(Advertising)
Overall confidence: 100%
Detected patterns
  • \.doubleclick\.net

(Analytics)
Overall confidence: 100%
Detected patterns
  • googletagmanager\.com/gtag/js

(Tag managers)
Overall confidence: 100%
Detected patterns
  • googletagmanager\.com/gtm\.js
  • \.googletagmanager\.com/

(Security)
Overall confidence: 100%
Detected patterns
  • ^https://[\w\d\.\-]+(?:\.dev)(?:/.+||/)$

(Advertising)
Overall confidence: 100%
Detected patterns
  • bat\.bing\.com/bat\.js
  • \w+

Page Statistics

52
Requests

98 %
HTTPS

0 %
IPv6

13
Domains

15
Subdomains

16
IPs

4
Countries

1271 kB
Transfer

3555 kB
Size

7
Cookies

Redirected requests

There were HTTP redirect chains for the following requests:

52 HTTP transactions Go Pro

Only in urlscan Pro

Inspect WebSocket connections, examine POST data effortlessly, and track overlap counts in real time. Features live search and filtering across all HTTP output, complete with full response metadata for deep analysis.
Click for more information
Free trials of urlscan Pro are available.

0 data transactions

Method
Protocol
Status Resource
Path
Size
x-fer
Time
Latency
Type
MIME-Type
IP
Location
GET
H2
200
Primary Request / Show response
termsandconditions-5wn.pages.dev/
167 KB
23 KB
491ms
127ms
Document
text/html
188.114.96.3
Cloudflare
General
Full URL
https://termsandconditions-5wn.pages.dev/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
188.114.96.3 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
6fa14e1612d83cbf85d02a06ca88d47e8c90c71545d27b292174ddd0073b4259
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

access-control-allow-origin
*
alt-svc
h3=":443"; ma=86400
cache-control
public, max-age=0, must-revalidate
cf-ray
a335f29fab0c8a3c-CPH
content-encoding
br
content-type
text/html; charset=utf-8
date
Sun, 30 Aug 2026 18:44:36 GMT
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
referrer-policy
strict-origin-when-cross-origin
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=UpZdFo9OcO%2FT2cCX3d8lqLC97yh3MmGYQABH%2Bb0SKyhZsbyaCzqBzwWSD8Jxyq4IT2u4ldINA1a1DUrrCKcngZphw5JyMVA8tiY4XzZ2dnJCu28rZuR3%2B62DT7rbYa49L6PRn%2BnGJofifnM%2FjV43psWzgA%3D%3D"}]}
server
cloudflare
x-content-type-options
nosniff
GET
H2
200
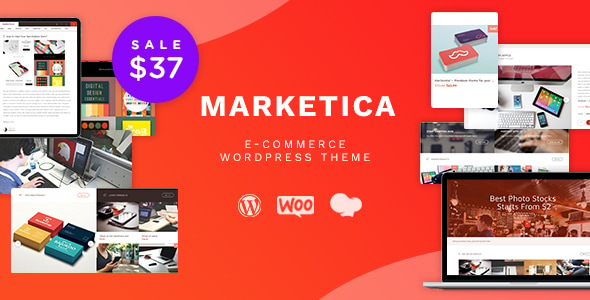
00-marketica-preview-sale37.__large_preview.jpg
market-resized.envatousercontent.com/themeforest.net/files/344043819/MARKETICA_PREVIEW/
70 KB
71 KB
92ms
37ms
Image
image/jpeg
172.64.146.183
Cloudflare
General
Full URL
https://market-resized.envatousercontent.com/themeforest.net/files/344043819/MARKETICA_PREVIEW/00-marketica-preview-sale37.__large_preview.jpg?auto=format&q=94&cf_fit=crop&gravity=top&h=8000&w=590&s=cc700268e0638344373c64d90d02d184c75d7defef1511b43f3ecf3627a3f2d4
Requested by
Host: termsandconditions-5wn.pages.dev
URL: https://termsandconditions-5wn.pages.dev/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.64.146.183 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
60360733662f006fbc87df4a1e92df08edf0785dc3e33130fc2b7ac0e3d7fbec
Security Headers
Name Value
Content-Security-Policy default-src 'none'; navigate-to 'none'; form-action 'none'; img-src data:;
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cf-cache-status
HIT
etag
"cfHmppIYSLtho11EMLfhIjWOhko7ufuBEJPsvhTJk_DQ:9305fa0bf667a6e3fe57dc5e2ec00dc7"
age
774940
cf-resized
internal=ram/- q=0 n=0+0 c=0+0 v=2026.2.12 l=72126
x-content-type-options
nosniff
alt-svc
h3=":443"; ma=86400
date
Sun, 30 Aug 2026 18:44:36 GMT
content-type
image/jpeg
last-modified
Wed, 11 Sep 2024 01:32:45 GMT
vary
accept
priority
u=1;i=?0,cf-chb=(264;u=3;i=?0 5829;u=5;i=?0 33564;u=6;i=?0)
content-security-policy
default-src 'none'; navigate-to 'none'; form-action 'none'; img-src data:;
cache-control
max-age=3600
cf-ray
a335f2a0d81a6c90-CPH
accept-ranges
bytes
content-length
72126
server
cloudflare
GET
H2
200
logos-20f56d7ae7a08da2c6698db678490c591ce302aedb1fcd05d3ad1e1484d3caf9.png
public-assets.envato-static.com/assets/generated_sprites/
55 KB
56 KB
199ms
89ms
Image
image/png
65.8.131.2
Amazon.com
General
Full URL
https://public-assets.envato-static.com/assets/generated_sprites/logos-20f56d7ae7a08da2c6698db678490c591ce302aedb1fcd05d3ad1e1484d3caf9.png
Requested by
Host: termsandconditions-5wn.pages.dev
URL: https://termsandconditions-5wn.pages.dev/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
65.8.131.2 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-65-8-131-2.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
6f8a015ab6d9602102f6c4dde38bf1a128f2647f20b76023c4793c2d3d86e57c

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

etag
"616011db88935edc6a2fef5c746a08c5"
age
26875350
access-control-allow-methods
GET
x-cache
Hit from cloudfront
x-amz-cf-id
fXAlpSeesJYxn0wSaZq1PR91CRFme4S-cAUpNVyVKYaCYSMR1O5ScQ==
date
Thu, 23 Oct 2025 17:22:07 GMT
content-type
image/png
vary
Access-Control-Request-Headers,Access-Control-Request-Method
last-modified
Mon, 20 Mar 2023 04:53:22 GMT
cache-control
max-age=315360000, public
via
1.1 8b6b9c8098dac83ebe6cded46eac0192.cloudfront.net (CloudFront)
accept-ranges
bytes
access-control-allow-origin
*
content-length
56337
x-amz-cf-pop
FRA60-P13
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H2
200
common-5af54247f3a645893af51456ee4c483f6530608e9c15ca4a8ac5a6e994d9a340.png
public-assets.envato-static.com/assets/generated_sprites/
10 KB
10 KB
34ms
33ms
Image
image/png
65.8.131.2
Amazon.com
General
Full URL
https://public-assets.envato-static.com/assets/generated_sprites/common-5af54247f3a645893af51456ee4c483f6530608e9c15ca4a8ac5a6e994d9a340.png
Requested by
Host: termsandconditions-5wn.pages.dev
URL: https://termsandconditions-5wn.pages.dev/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
65.8.131.2 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-65-8-131-2.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
14f8bc60470b39265fe5c01e92035209bd04b91cd7da99d59ca3ccd9de5eac62

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

etag
"64089c65cdcb56ecdfdcccb445fb844c"
age
8425478
access-control-allow-methods
GET
x-cache
Hit from cloudfront
x-amz-cf-id
9QU2ONX4fDZtTFWnbV9StZFWdoZo3OeKH2fIpSbyMJfUpvkeRQMBDA==
date
Mon, 25 May 2026 06:19:59 GMT
content-type
image/png
vary
Access-Control-Request-Headers,Access-Control-Request-Method
last-modified
Mon, 20 Mar 2023 04:53:22 GMT
cache-control
max-age=315360000, public
via
1.1 8b6b9c8098dac83ebe6cded46eac0192.cloudfront.net (CloudFront)
accept-ranges
bytes
access-control-allow-origin
*
content-length
9797
x-amz-cf-pop
FRA60-P13
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H2
200
index-999d91c45b3ce6e6c7409b80cb1734b55d9f0a30546d926e1f2c262cd719f9c7.css
public-assets.envato-static.com/assets/market/core/
195 KB
34 KB
140ms
37ms
Stylesheet
text/css
65.8.131.2
Amazon.com
General
Full URL
https://public-assets.envato-static.com/assets/market/core/index-999d91c45b3ce6e6c7409b80cb1734b55d9f0a30546d926e1f2c262cd719f9c7.css
Requested by
Host: termsandconditions-5wn.pages.dev
URL: https://termsandconditions-5wn.pages.dev/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
65.8.131.2 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-65-8-131-2.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
9d22b4007cc21a935e65245bd8090214db4fc3eed3aecdd1d455cd154f78612a

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
W/"90c3cbf79d4b328d0f6ab5902ed82178"
age
7878387
access-control-allow-methods
GET
x-cache
Hit from cloudfront
x-amz-cf-id
qdpKSMGvYHCbNvFVPczt1YqpnYtidrBzpf90EupghmLcnmP7-j1RTg==
date
Sun, 31 May 2026 14:18:10 GMT
content-type
text/css
vary
Access-Control-Request-Headers,Access-Control-Request-Method,Accept-Encoding
last-modified
Wed, 02 Apr 2025 09:08:38 GMT
cache-control
max-age=315360000, public
via
1.1 8b6b9c8098dac83ebe6cded46eac0192.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-amz-cf-pop
FRA60-P13
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H2
200
index-ffa1c54dffd67e25782769d410efcfaa8c68b66002df4c034913ae320bfe6896.css
public-assets.envato-static.com/assets/market/pages/default/
225 KB
42 KB
168ms
64ms
Stylesheet
text/css
65.8.131.2
Amazon.com
General
Full URL
https://public-assets.envato-static.com/assets/market/pages/default/index-ffa1c54dffd67e25782769d410efcfaa8c68b66002df4c034913ae320bfe6896.css
Requested by
Host: termsandconditions-5wn.pages.dev
URL: https://termsandconditions-5wn.pages.dev/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
65.8.131.2 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-65-8-131-2.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
5248900f1317a0f8cab40d0a15332adc13d7906bb0df4ef1c33c4438b87ae335

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
W/"ad6cbd68ce100101dcce511eb0e337bd"
age
6254063
access-control-allow-methods
GET
x-cache
Hit from cloudfront
x-amz-cf-id
rmlAZlMqXiRQUepa4YSWJwy_opxiCVUMvYAOkyFC3iWBJ_QlEiwiNw==
date
Fri, 19 Jun 2026 09:30:14 GMT
content-type
text/css
vary
Access-Control-Request-Headers,Access-Control-Request-Method,Accept-Encoding
last-modified
Thu, 27 Mar 2025 23:59:36 GMT
cache-control
max-age=315360000, public
via
1.1 8b6b9c8098dac83ebe6cded46eac0192.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-amz-cf-pop
FRA60-P13
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H2
200
brand_neue_tokens-f25ae27cb18329d3bba5e95810e5535514237937774fca40a02d8e2635fa20d6.js Show response
public-assets.envato-static.com/assets/components/
43 KB
7 KB
35ms
34ms
Script
application/javascript
65.8.131.2
Amazon.com
General
Full URL
https://public-assets.envato-static.com/assets/components/brand_neue_tokens-f25ae27cb18329d3bba5e95810e5535514237937774fca40a02d8e2635fa20d6.js
Requested by
Host: termsandconditions-5wn.pages.dev
URL: https://termsandconditions-5wn.pages.dev/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
65.8.131.2 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-65-8-131-2.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
8adad9ee9ef1b7fa392ee2d5a769d3f43a9462bed8e3d8be57c02faa332bc244

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
W/"ab76a62991ebf1681f0ebf84c616185f"
age
6658639
access-control-allow-methods
GET
x-cache
Hit from cloudfront
x-amz-cf-id
j2wBbVId2lCMnsBJRn_bRV0taQ6aBoDh4gFtPDJQUYNuEAi4FhSbiQ==
date
Sun, 14 Jun 2026 17:07:18 GMT
content-type
application/javascript
vary
Access-Control-Request-Headers,Access-Control-Request-Method,Accept-Encoding
last-modified
Mon, 28 Jul 2025 09:13:15 GMT
cache-control
max-age=315360000, public
via
1.1 8b6b9c8098dac83ebe6cded46eac0192.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-amz-cf-pop
FRA60-P13
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H2
200
head-d4f3da877553664cb1d5ed45cb42c6ec7e6b00d0c4d164be8747cfd5002a24eb.js Show response
public-assets.envato-static.com/assets/market/core/
10 KB
5 KB
179ms
76ms
Script
application/javascript
65.8.131.2
Amazon.com
General
Full URL
https://public-assets.envato-static.com/assets/market/core/head-d4f3da877553664cb1d5ed45cb42c6ec7e6b00d0c4d164be8747cfd5002a24eb.js
Requested by
Host: termsandconditions-5wn.pages.dev
URL: https://termsandconditions-5wn.pages.dev/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
65.8.131.2 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-65-8-131-2.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
dbf8c90e7cdc155dfc29a7f760e9efafa41e8a3a5a19c3320b995687d6ddff51

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
W/"39e854fe45d3aca8ae69fdf4d91e7ba0"
age
7518875
access-control-allow-methods
GET
x-cache
Hit from cloudfront
x-amz-cf-id
lR_swnphBFRcpI_0iQ3yD7UKR_L7tdzWrmldR6uPLkdn3ZHMeICP5Q==
date
Thu, 04 Jun 2026 18:10:01 GMT
content-type
application/javascript
vary
Access-Control-Request-Headers,Access-Control-Request-Method,Accept-Encoding
last-modified
Mon, 28 Jul 2025 02:40:12 GMT
cache-control
max-age=315360000, public
via
1.1 8b6b9c8098dac83ebe6cded46eac0192.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-amz-cf-pop
FRA60-P13
server
AmazonS3
x-amz-server-side-encryption
AES256
GET

wp-emoji-release-version.2.7.js
wptheme.cloud/wp-includes/wp-elements/
0
0


GET
H2
200
16005611.js Show response
bat.bing.com/p/action/
397 B
698 B
431ms
37ms
Script
application/javascript
150.171.27.10
Microsoft Corpora...
General
Full URL
https://bat.bing.com/p/action/16005611.js
Requested by
Host: termsandconditions-5wn.pages.dev
URL: https://termsandconditions-5wn.pages.dev/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
150.171.27.10 , United States, ASN8075 (MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation, US),
Reverse DNS
Software
/
Resource Hash
e36cd50b6c1410f6efe1091b16f6d846e8ac00beb26d5ea265b401a2fc40360a
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains; preload
cache-control
private,max-age=1800
content-encoding
br
accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Mobile, Sec-CH-UA-Model, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
x-msedge-ref
Ref A: B89F50C58AFF48009675F95C0797A3A7 Ref B: CPH011050219062 Ref C: 2026-08-30T18:44:37Z
cross-origin-resource-policy
cross-origin
x-cache
CONFIG_NOCACHE
date
Sun, 30 Aug 2026 18:44:36 GMT
content-type
application/javascript; charset=utf-8
vary
Accept-Encoding
GET
H2
200
pc.js Show response
g.lzd-cdn.org/g/mtb/lib-mtop/2.5.1/polyfillB.js,mtb/lib-promise/3.1.3/mtop.js,mtb/lib-modules/1.1.4/
2 KB
2 KB
162ms
39ms
Script
application/javascript
3.9.176.51
Amazon.com
General
Full URL
https://g.lzd-cdn.org/g/mtb/lib-mtop/2.5.1/polyfillB.js,mtb/lib-promise/3.1.3/mtop.js,mtb/lib-modules/1.1.4/pc.js
Requested by
Host: termsandconditions-5wn.pages.dev
URL: https://termsandconditions-5wn.pages.dev/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
3.9.176.51 City of London, United Kingdom, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-3-9-176-51.eu-west-2.compute.amazonaws.com
Software
/
Resource Hash
c401d80a6dd4c3266b32934928ed11ddd1d06939c6758bfd837416eb0ee3b58a

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-store
access-control-expose-headers
*
timing-allow-origin
*
accept-ch
Sec-CH-UA-Platform-Version, Sec-CH-UA-Model, Sec-CH-UA-Full-Version-List
etag
W/"7dc-bCL+7sO3aVY4dGciumsQRvMsfUI"
access-control-allow-origin
*
content-length
2012
date
Sun, 30 Aug 2026 18:44:36 GMT
content-type
application/javascript; charset=utf-8
GET
H2
200
gtm_measurements-40b0a0f82bafab0a0bb77fc35fe1da0650288300b85126c95b4676bcff6e4584.js Show response
public-assets.envato-static.com/assets/
15 KB
4 KB
176ms
73ms
Script
application/javascript
65.8.131.2
Amazon.com
General
Full URL
https://public-assets.envato-static.com/assets/gtm_measurements-40b0a0f82bafab0a0bb77fc35fe1da0650288300b85126c95b4676bcff6e4584.js
Requested by
Host: termsandconditions-5wn.pages.dev
URL: https://termsandconditions-5wn.pages.dev/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
65.8.131.2 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-65-8-131-2.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
6328e6b9e5c4f7ac64d124dde5d2b9412efdf0988ea4fb8bc156d501ff44216a

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
W/"307bf47f6520bddf111a6d729296777a"
age
7084172
access-control-allow-methods
GET
x-cache
Hit from cloudfront
x-amz-cf-id
MYWGNd-X8_7Vz50FSx-TBtuX74Y_i_hQ43mTXaoYUym_U0JPEvMHlw==
date
Tue, 09 Jun 2026 18:55:05 GMT
content-type
application/javascript
vary
Access-Control-Request-Headers,Access-Control-Request-Method,Accept-Encoding
last-modified
Mon, 28 Jul 2025 08:46:57 GMT
cache-control
max-age=315360000, public
via
1.1 8b6b9c8098dac83ebe6cded46eac0192.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-amz-cf-pop
FRA60-P13
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H2
401
bKtCv_wd5nyx.png
res.cloudinary.com/db5uodec1/image/upload/v1758211590/
0
357 B
587ms
218ms
Image
image/gif
151.101.193.137
Fastly
General
Full URL
https://res.cloudinary.com/db5uodec1/image/upload/v1758211590/bKtCv_wd5nyx.png
Requested by
Host: termsandconditions-5wn.pages.dev
URL: https://termsandconditions-5wn.pages.dev/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.137 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
Cloudinary /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=604800

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=604800
cache-control
private, no-transform, max-age=0, no-cache
timing-allow-origin
*
access-control-expose-headers
Content-Length,Content-Disposition,Server-Timing,X-Cld-Error
pragma
no-cache
content-transfer-encoding
binary
accept-ranges
bytes
x-cld-error
cloud_name db5uodec1 is disabled
server-timing
cld-fastly;mitm=p;dur=199;cpu=0;start=2026-08-30T18:44:36.935Z;desc=hit,rtt;dur=17
content-length
0
access-control-allow-origin
*
date
Sun, 30 Aug 2026 18:44:37 GMT
content-disposition
inline
content-type
image/gif
server
Cloudinary
GET
H2
200
badge-a65149663b95bcee411e80ccf4da9788f174155587980d8f1d9c44fd8b59edd8.svg
public-assets.envato-static.com/assets/header/
942 B
1 KB
36ms
35ms
Image
image/svg+xml
65.8.131.2
Amazon.com
General
Full URL
https://public-assets.envato-static.com/assets/header/badge-a65149663b95bcee411e80ccf4da9788f174155587980d8f1d9c44fd8b59edd8.svg
Requested by
Host: termsandconditions-5wn.pages.dev
URL: https://termsandconditions-5wn.pages.dev/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
65.8.131.2 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-65-8-131-2.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
ea3a60ea39171409e4f531bab81dc0a0f23d5ab62c5bbc2160599b766c5803dd

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

etag
"fc7c25448914bb4233c91cd6a96eeeea"
age
8548679
access-control-allow-methods
GET
x-cache
Hit from cloudfront
x-amz-cf-id
oy0lFAI163NVG1kSM_N3C3NJqjKxfjAqlHZL6mvrIFYmKt8rIoJnaA==
date
Sat, 23 May 2026 20:06:38 GMT
content-type
image/svg+xml
vary
Access-Control-Request-Headers,Access-Control-Request-Method
last-modified
Tue, 30 Jul 2024 07:08:22 GMT
cache-control
max-age=315360000, public
via
1.1 8b6b9c8098dac83ebe6cded46eac0192.cloudfront.net (CloudFront)
accept-ranges
bytes
access-control-allow-origin
*
content-length
942
x-amz-cf-pop
FRA60-P13
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H2
200
thumbs_up-e5ce4c821cfd6a6aeba61127a8e8c4d2d7c566e654f588a22708c64d66680869.svg
public-assets.envato-static.com/assets/header/
994 B
1 KB
37ms
36ms
Image
image/svg+xml
65.8.131.2
Amazon.com
General
Full URL
https://public-assets.envato-static.com/assets/header/thumbs_up-e5ce4c821cfd6a6aeba61127a8e8c4d2d7c566e654f588a22708c64d66680869.svg
Requested by
Host: termsandconditions-5wn.pages.dev
URL: https://termsandconditions-5wn.pages.dev/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
65.8.131.2 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-65-8-131-2.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
3314bbeb196f5f1858b98256fe14b1bbe632f6b4077d311139e8173f3cfc2945

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

etag
"0d3e22e992abcb39985d915acba0f7cc"
age
24359502
access-control-allow-methods
GET
x-cache
Hit from cloudfront
x-amz-cf-id
kRFaQ5Ufn4BSc_AVfOf5-F2OX_Zc_-GOCLX2rqLlqV9_U8m0W_vcBw==
date
Fri, 21 Nov 2025 20:12:55 GMT
content-type
image/svg+xml
vary
Access-Control-Request-Headers,Access-Control-Request-Method
last-modified
Tue, 30 Jul 2024 07:08:22 GMT
cache-control
max-age=315360000, public
via
1.1 8b6b9c8098dac83ebe6cded46eac0192.cloudfront.net (CloudFront)
accept-ranges
bytes
access-control-allow-origin
*
content-length
994
x-amz-cf-pop
FRA60-P13
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H2
200
32d9570e977084da95ac9203c3299a52.jpg
i.pinimg.com/736x/32/d9/57/
73 KB
74 KB
520ms
152ms
Image
image/jpeg
151.101.192.84
Fastly
General
Full URL
https://i.pinimg.com/736x/32/d9/57/32d9570e977084da95ac9203c3299a52.jpg
Requested by
Host: termsandconditions-5wn.pages.dev
URL: https://termsandconditions-5wn.pages.dev/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.192.84 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
/
Resource Hash
29a010cf21230d20587e431ec9153c928fee096d9bf6740815c96fa93ddc0d21

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000, immutable
etag
"880db2181bcfd42819079412fb3f257e"
x-cdn
fastly
accept-ranges
bytes
server-timing
cdn;desc="fastly", cdn-cache;desc="HIT, MISS", cdn-edge-time;dur=134
alt-svc
h3=":443";ma=604800
content-length
75031
date
Sun, 30 Aug 2026 18:44:37 GMT
content-type
image/jpeg
vary
Origin
x-amz-server-side-encryption
AES256
GET
H/1.1
200
OK
1.gif
imgsct.cookiebot.com/
35 B
778 B
446ms
44ms
Image
image/gif
104.81.4.96
Akamai Technologies
General
Full URL
https://imgsct.cookiebot.com/1.gif?dgi=d10f7659-aa82-4007-9cf1-54a9496002bf
Requested by
Host: termsandconditions-5wn.pages.dev
URL: https://termsandconditions-5wn.pages.dev/
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_256_GCM
Server
104.81.4.96 Berlin, Germany, ASN16625 (AKAMAI-AS - Akamai Technologies, Inc., US),
Reverse DNS
a104-81-4-96.deploy.static.akamaitechnologies.com
Software
UploadServer /
Resource Hash
6adc3d4c1056996e4e8b765a62604c78b1f867cceb3b15d0b9bedb7c4857f992

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
Access-Control-Expose-Headers
*
x-goog-hash
crc32c=rX4K2g==, md5=whlt6LpBLGDCKrSRr3sUCQ==
ETag
"c2196de8ba412c60c22ab491af7b1409"
x-goog-stored-content-encoding
identity
x-goog-stored-content-length
35
Date
Sun, 30 Aug 2026 18:44:37 GMT
Last-Modified
Mon, 23 Oct 2023 11:39:32 GMT
Content-Type
image/gif
X-GUploader-UploadID
AJjja9aY4SCKWAHdFSTcxshhd0eAK0zg785-VdNdWzLEmRfTu6Cb4MZ9ub-nBAM5C2mj_MeN
Cache-Control
public,max-age=1800
x-goog-storage-class
STANDARD
Cross-Origin-Resource-Policy
cross-origin
Connection
keep-alive
Accept-Ranges
bytes
Access-Control-Allow-Origin
*
x-goog-generation
1698061172769999
Content-Length
35
Server
UploadServer
GET
H2
204
0
bat.bing.com/action/
0
288 B
450ms
56ms
Image
text/plain
150.171.27.10
Microsoft Corpora...
General
Full URL
https://bat.bing.com/action/0?ti=16005611&tm=gtm002&Ver=2&mid=bb77e21d-0c6c-42c3-ba87-fe2355ba6056&bo=2&sid=422440906d3c11f083cb21e95f31b0ab&vid=422465806d3c11f091d599aa9de8ebcb&vids=0&msclkid=N&uach=pv%3D19.0.0&pi=918639831&lg=en-US&sw=1920&sh=1080&sc=24&tl=Marketica%20-%20eCommerce%20and%20Marketplace%20-%20WooCommerce%20WordPress%20Theme%20by%20tokopress&p=https%3A%2F%2Fthemeforest.net%2Fitem%2Fmarketica-marketplace-wordpress-theme%2F8988002%3Fsrsltid%3DAfmBOorwNEgJi-iQXu--3qzSatNlhXMhGjZ-gMFxbyMWP2LkJDdESL9b&r=https%3A%2F%2Fwww.google.com%2F&lt=4778&evt=pageLoad&sv=1&asc=G&cdb=AQIT&rn=643027
Requested by
Host: termsandconditions-5wn.pages.dev
URL: https://termsandconditions-5wn.pages.dev/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
150.171.27.10 , United States, ASN8075 (MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation, US),
Reverse DNS
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains; preload
cache-control
no-cache, must-revalidate
pragma
no-cache
accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Mobile, Sec-CH-UA-Model, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
x-msedge-ref
Ref A: A70A90C2D55B4BE7AE1FC21E23922F33 Ref B: CPH011050219062 Ref C: 2026-08-30T18:44:37Z
expires
Fri, 01 Jan 1990 00:00:00 GMT
access-control-allow-origin
*
x-cache
CONFIG_NOCACHE
date
Sun, 30 Aug 2026 18:44:36 GMT
GET
H2
200
normalize-b1a155928b172f008fc543e8a057fcbe0f8855c5f410811adcaf2cf21f310a63.css
public-assets.envato-static.com/assets/normalize.css/
2 KB
1 KB
54ms
54ms
Stylesheet
text/css
65.8.131.2
Amazon.com
General
Full URL
https://public-assets.envato-static.com/assets/normalize.css/normalize-b1a155928b172f008fc543e8a057fcbe0f8855c5f410811adcaf2cf21f310a63.css
Requested by
Host: public-assets.envato-static.com
URL: https://public-assets.envato-static.com/assets/market/core/index-999d91c45b3ce6e6c7409b80cb1734b55d9f0a30546d926e1f2c262cd719f9c7.css
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
65.8.131.2 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-65-8-131-2.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
6a2810521190291abcf97c153fee9ffe8846cb04c087f23e7d1eb56b5db836fd

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://public-assets.envato-static.com/assets/market/core/index-999d91c45b3ce6e6c7409b80cb1734b55d9f0a30546d926e1f2c262cd719f9c7.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
W/"99bae955c01ebc079ddfc65f16db5e63"
age
6654944
access-control-allow-methods
GET
x-cache
Hit from cloudfront
x-amz-cf-id
8F9hqnRpp5zkDijoSEYOPtzta2wgoel90e3M856UxCsTAjM1--ytBA==
date
Sun, 14 Jun 2026 18:08:53 GMT
content-type
text/css
vary
Access-Control-Request-Headers,Access-Control-Request-Method,Accept-Encoding
last-modified
Thu, 10 Oct 2024 02:29:38 GMT
cache-control
max-age=315360000, public
via
1.1 8b6b9c8098dac83ebe6cded46eac0192.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-amz-cf-pop
FRA60-P13
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H2
200
gtm.js Show response
www.googletagmanager.com/
374 KB
128 KB
500ms
85ms
Script
application/javascript
142.251.20.97
Google LLC
General
Full URL
https://www.googletagmanager.com/gtm.js?id=GTM-W8KL5Q5
Requested by
Host: termsandconditions-5wn.pages.dev
URL: https://termsandconditions-5wn.pages.dev/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.20.97 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bx-in-f97.1e100.net
Software
Google Tag Manager /
Resource Hash
071b9668932fc901d7f779ee9bfd9b05a30bcde960751a66ff8b586d9d051fc2
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
zstd
expires
Sun, 30 Aug 2026 18:44:37 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sun, 30 Aug 2026 18:44:37 GMT
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
last-modified
Sun, 30 Aug 2026 18:00:00 GMT
access-control-allow-headers
Cache-Control
strict-transport-security
max-age=31536000; includeSubDomains
cache-control
private, max-age=900
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
access-control-allow-origin
*
content-length
130213
x-xss-protection
0
server
Google Tag Manager
GET
H2
200
gtm.js Show response
www.googletagmanager.com/
430 KB
150 KB
555ms
140ms
Script
application/javascript
142.251.20.97
Google LLC
General
Full URL
https://www.googletagmanager.com/gtm.js?id=GTM-KGCDGPL6
Requested by
Host: termsandconditions-5wn.pages.dev
URL: https://termsandconditions-5wn.pages.dev/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.20.97 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bx-in-f97.1e100.net
Software
Google Tag Manager /
Resource Hash
8dd050ef03bd01da25a5b5d25e02940fce69bd9accd49e3baae50d46a532d70c
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
zstd
expires
Sun, 30 Aug 2026 18:44:37 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sun, 30 Aug 2026 18:44:37 GMT
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
last-modified
Sun, 30 Aug 2026 18:00:00 GMT
access-control-allow-headers
Cache-Control
strict-transport-security
max-age=31536000; includeSubDomains
cache-control
private, max-age=900
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
access-control-allow-origin
*
content-length
153319
x-xss-protection
0
server
Google Tag Manager
GET
H2
401
bKtCv_wd5nyx.png
res.cloudinary.com/db5uodec1/image/upload/v1758211590/
0
93 B
214ms
19ms
Image
image/gif
151.101.193.137
Fastly
General
Full URL
https://res.cloudinary.com/db5uodec1/image/upload/v1758211590/bKtCv_wd5nyx.png
Requested by
Host: termsandconditions-5wn.pages.dev
URL: https://termsandconditions-5wn.pages.dev/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.137 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
Cloudinary /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=604800

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=604800
cache-control
private, no-transform, max-age=0, no-cache
timing-allow-origin
*
access-control-expose-headers
Content-Length,Content-Disposition,Server-Timing,X-Cld-Error
pragma
no-cache
content-transfer-encoding
binary
accept-ranges
bytes
x-cld-error
cloud_name db5uodec1 is disabled
server-timing
cld-fastly;mitm=p;dur=1;cpu=0;start=2026-08-30T18:44:37.154Z;desc=hit,rtt;dur=17
content-length
0
access-control-allow-origin
*
date
Sun, 30 Aug 2026 18:44:37 GMT
content-disposition
inline
content-type
image/gif
server
Cloudinary
GET
H2
200
bc-v4.min.html Show response
consentcdn.cookiebot.com/sdk/ Frame CBBD
627 B
811 B
404ms
31ms
Document
text/html
23.215.20.211
Akamai Technologies
General
Full URL
https://consentcdn.cookiebot.com/sdk/bc-v4.min.html
Requested by
Host: termsandconditions-5wn.pages.dev
URL: https://termsandconditions-5wn.pages.dev/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
23.215.20.211 Frankfurt am Main, Germany, ASN16625 (AKAMAI-AS - Akamai Technologies, Inc., US),
Reverse DNS
a23-215-20-211.deploy.static.akamaitechnologies.com
Software
AkamaiNetStorage /
Resource Hash
738e5435f2d18427d291a0d6289eee0ebbc87b596d6003919f255760ac293104

Request headers

Referer
https://termsandconditions-5wn.pages.dev/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

accept-ranges
bytes
cache-control
max-age=31461644
content-encoding
gzip
content-length
392
content-type
text/html
cross-origin-embedder-policy
require-corp
cross-origin-resource-policy
cross-origin
date
Sun, 30 Aug 2026 18:44:37 GMT
etag
"3d08665fa4c7bcf9fa2dcbbc7efe1d0f:1649057029.895163"
expires
Sun, 29 Aug 2027 22:05:21 GMT
last-modified
Mon, 04 Apr 2022 07:23:49 GMT
server
AkamaiNetStorage
server-timing
cdn-cache; desc=HIT edge; dur=1 ak_p; desc="1788115477312_34911175_571044122_12_424_30_33_255";dur=1
vary
Accept-Encoding
x-akamai-transformed
9 - 0 pmb=mRUM,1
GET
H2
404
953691586 Show response
td.doubleclick.net/td/rul/ Frame AFF5
2 KB
2 KB
583ms
151ms
Document
text/html
142.251.20.157
Google LLC
General
Full URL
https://td.doubleclick.net/td/rul/953691586?random=1753876666537&cv=11&fst=1753876666537&fmt=3&bg=ffffff&guid=ON&async=1&en=gtag.config&gtm=45be57s1z89195929391za200zb9195929391zd9195929391&gcd=13n3n3n3n5l1&dma=0&tag_exp=101509157~103116026~103200004~103233427~104684208~104684211~104948813~105103161~105103163~105124543~105124545&u_w=1920&u_h=1080&url=https%3A%2F%2Fthemeforest.net%2Fitem%2Fmarketica-marketplace-wordpress-theme%2F8988002%3Fsrsltid%3DAfmBOorwNEgJi-iQXu--3qzSatNlhXMhGjZ-gMFxbyMWP2LkJDdESL9b&ref=https%3A%2F%2Fwww.google.com%2F&hn=www.googleadservices.com&frm=0&tiba=Marketica%20-%20eCommerce%20and%20Marketplace%20-%20WooCommerce%20WordPress%20Theme%20by%20tokopress&npa=0&us_privacy=1---&pscdl=noapi&auid=786247872.1753876602&uaa=x86&uab=64&uafvl=Not)A%253BBrand%3B8.0.0.0%7CChromium%3B138.0.7204.183%7CGoogle%2520Chrome%3B138.0.7204.183&uamb=0&uam=&uap=Windows&uapv=19.0.0&uaw=0&fledge=1&data=event%3Dgtag.config
Requested by
Host: termsandconditions-5wn.pages.dev
URL: https://termsandconditions-5wn.pages.dev/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.20.157 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bx-in-f157.1e100.net
Software
/
Resource Hash
c42844045ae09380561d14fd2e5ee08454fd46b9d3f6ebeea4a19c6e7a7fe2ca

Request headers

Referer
https://termsandconditions-5wn.pages.dev/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
1577
content-type
text/html; charset=UTF-8
date
Sun, 30 Aug 2026 18:44:37 GMT
referrer-policy
no-referrer
GET
H2
404
943617023 Show response
td.doubleclick.net/td/rul/ Frame C949
2 KB
2 KB
578ms
152ms
Document
text/html
142.251.20.157
Google LLC
General
Full URL
https://td.doubleclick.net/td/rul/943617023?random=1753876666603&cv=11&fst=1753876666603&fmt=3&bg=ffffff&guid=ON&async=1&en=gtag.config&gtm=45be57s1v889115050z89195929391za200zb9195929391zd9195929391&gcd=13n3n3n3n5l1&dma=0&tag_exp=101509157~103116026~103200004~103233427~104684208~104684211~104948813~105103161~105103163~105124543~105124545&u_w=1920&u_h=1080&url=https%3A%2F%2Fthemeforest.net%2Fitem%2Fmarketica-marketplace-wordpress-theme%2F8988002%3Fsrsltid%3DAfmBOorwNEgJi-iQXu--3qzSatNlhXMhGjZ-gMFxbyMWP2LkJDdESL9b&ref=https%3A%2F%2Fwww.google.com%2F&hn=www.googleadservices.com&frm=0&tiba=Marketica%20-%20eCommerce%20and%20Marketplace%20-%20WooCommerce%20WordPress%20Theme%20by%20tokopress&npa=0&us_privacy=1---&pscdl=noapi&auid=786247872.1753876602&uaa=x86&uab=64&uafvl=Not)A%253BBrand%3B8.0.0.0%7CChromium%3B138.0.7204.183%7CGoogle%2520Chrome%3B138.0.7204.183&uamb=0&uam=&uap=Windows&uapv=19.0.0&uaw=0&fledge=1&data=event%3Dgtag.config
Requested by
Host: termsandconditions-5wn.pages.dev
URL: https://termsandconditions-5wn.pages.dev/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.20.157 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bx-in-f157.1e100.net
Software
/
Resource Hash
8ba45b7315225b2246e1b7408f1d742f195bfc1713b384af8b65a04c1f8e5454

Request headers

Referer
https://termsandconditions-5wn.pages.dev/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
1577
content-type
text/html; charset=UTF-8
date
Sun, 30 Aug 2026 18:44:37 GMT
referrer-policy
no-referrer
GET
H2
404
943617023 Show response
td.doubleclick.net/td/rul/ Frame 35EB
2 KB
2 KB
582ms
157ms
Document
text/html
142.251.20.157
Google LLC
General
Full URL
https://td.doubleclick.net/td/rul/943617023?random=1753876666631&cv=11&fst=1753876666631&fmt=3&bg=ffffff&guid=ON&async=1&gtm=45be57s1v889115050z89195929391za200zb9195929391zd9195929391&gcd=13n3n3n3n5l1&dma=0&tag_exp=101509157~103116026~103200004~103233427~104684208~104684211~104948813~105103161~105103163~105124543~105124545&u_w=1920&u_h=1080&url=https%3A%2F%2Fthemeforest.net%2Fitem%2Fmarketica-marketplace-wordpress-theme%2F8988002%3Fsrsltid%3DAfmBOorwNEgJi-iQXu--3qzSatNlhXMhGjZ-gMFxbyMWP2LkJDdESL9b&ref=https%3A%2F%2Fwww.google.com%2F&hn=www.googleadservices.com&frm=0&tiba=Marketica%20-%20eCommerce%20and%20Marketplace%20-%20WooCommerce%20WordPress%20Theme%20by%20tokopress&did=dMWZhNz&gdid=dMWZhNz&npa=0&us_privacy=1---&pscdl=noapi&auid=786247872.1753876602&uaa=x86&uab=64&uafvl=Not)A%253BBrand%3B8.0.0.0%7CChromium%3B138.0.7204.183%7CGoogle%2520Chrome%3B138.0.7204.183&uamb=0&uam=&uap=Windows&uapv=19.0.0&uaw=0&fledge=1&_tu=Cg&data=ads_data_redaction%3Dfalse
Requested by
Host: termsandconditions-5wn.pages.dev
URL: https://termsandconditions-5wn.pages.dev/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.20.157 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bx-in-f157.1e100.net
Software
/
Resource Hash
8ba45b7315225b2246e1b7408f1d742f195bfc1713b384af8b65a04c1f8e5454

Request headers

Referer
https://termsandconditions-5wn.pages.dev/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
1577
content-type
text/html; charset=UTF-8
date
Sun, 30 Aug 2026 18:44:37 GMT
referrer-policy
no-referrer
GET
H2
200
marketplace-glyphs-85cc828ca8d675d6613f41b266689cea348332a12f6966cbe08583f16f208a40.woff
public-assets.envato-static.com/assets/marketplace-glyphs/
12 KB
12 KB
93ms
32ms
Font
application/font-woff
65.8.131.2
Amazon.com
General
Full URL
https://public-assets.envato-static.com/assets/marketplace-glyphs/marketplace-glyphs-85cc828ca8d675d6613f41b266689cea348332a12f6966cbe08583f16f208a40.woff
Requested by
Host: public-assets.envato-static.com
URL: https://public-assets.envato-static.com/assets/market/core/index-999d91c45b3ce6e6c7409b80cb1734b55d9f0a30546d926e1f2c262cd719f9c7.css
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
65.8.131.2 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-65-8-131-2.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
89c24d697618dd08e5585cc2dc210afe6b8d89e547453a05e19b6a7c91fe73b6

Request headers

Origin
https://termsandconditions-5wn.pages.dev
sec-ch-ua-platform
"Linux"
Referer
https://public-assets.envato-static.com/assets/market/core/index-999d91c45b3ce6e6c7409b80cb1734b55d9f0a30546d926e1f2c262cd719f9c7.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

etag
"c2f2baaae5f1514a97df13472e3bed86"
age
6354325
access-control-allow-methods
GET
x-cache
Hit from cloudfront
x-amz-cf-id
pp8c8YubkkeL45N-Ej6pKzLlO_bJz5DVcfD0ascqgVc1zWNpe5Qxyw==
date
Thu, 18 Jun 2026 05:39:13 GMT
content-type
application/font-woff
vary
Access-Control-Request-Headers,Access-Control-Request-Method
last-modified
Mon, 20 Mar 2023 04:53:25 GMT
cache-control
max-age=315360000, public
via
1.1 af5022f8a81a8454aba56777e50d3c58.cloudfront.net (CloudFront)
accept-ranges
bytes
access-control-allow-origin
*
content-length
12076
x-amz-cf-pop
FRA60-P13
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H2
200
logo-bcorp-e83f7da84188b8edac311fbf08eaa86634e9db7c67130cdc17837c1172c5f678.svg
public-assets.envato-static.com/assets/header-footer/
11 KB
5 KB
35ms
33ms
Image
image/svg+xml
65.8.131.2
Amazon.com
General
Full URL
https://public-assets.envato-static.com/assets/header-footer/logo-bcorp-e83f7da84188b8edac311fbf08eaa86634e9db7c67130cdc17837c1172c5f678.svg
Requested by
Host: termsandconditions-5wn.pages.dev
URL: https://termsandconditions-5wn.pages.dev/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
65.8.131.2 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-65-8-131-2.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
6902a46cd3be583fdda26df9df6a07d8c4d2fbecc4bfaa685c1884e396122eb2

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
W/"a41c2e8cd861b1d1cf0184941ab679e0"
age
20916685
access-control-allow-methods
GET
x-cache
Hit from cloudfront
x-amz-cf-id
TYyXBqwvTnK_VhDb4O2OrDhHVoN65bUX1mtX3wWDkvDSBuB175b44w==
date
Wed, 31 Dec 2025 16:33:13 GMT
content-type
image/svg+xml
vary
Access-Control-Request-Headers,Access-Control-Request-Method,accept-encoding
last-modified
Tue, 30 Jul 2024 07:08:22 GMT
cache-control
max-age=315360000, public
via
1.1 8b6b9c8098dac83ebe6cded46eac0192.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-amz-cf-pop
FRA60-P13
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H2
404
800411572 Show response
td.doubleclick.net/td/rul/ Frame A3CC
2 KB
2 KB
550ms
153ms
Document
text/html
142.251.20.157
Google LLC
General
Full URL
https://td.doubleclick.net/td/rul/800411572?random=1753876666684&cv=11&fst=1753876666684&fmt=3&bg=ffffff&guid=ON&async=1&en=gtag.config&gtm=45be57s1v896649154z89195929391za200zb9195929391zd9195929391&gcd=13n3n3n3n5l1&dma=0&tag_exp=101509157~103116026~103200004~103233427~104684208~104684211~104948813~105087538~105087540~105103161~105103163~105124543~105124545&u_w=1920&u_h=1080&url=https%3A%2F%2Fthemeforest.net%2Fitem%2Fmarketica-marketplace-wordpress-theme%2F8988002%3Fsrsltid%3DAfmBOorwNEgJi-iQXu--3qzSatNlhXMhGjZ-gMFxbyMWP2LkJDdESL9b&ref=https%3A%2F%2Fwww.google.com%2F&hn=www.googleadservices.com&frm=0&tiba=Marketica%20-%20eCommerce%20and%20Marketplace%20-%20WooCommerce%20WordPress%20Theme%20by%20tokopress&npa=0&us_privacy=1---&pscdl=noapi&auid=786247872.1753876602&uaa=x86&uab=64&uafvl=Not)A%253BBrand%3B8.0.0.0%7CChromium%3B138.0.7204.183%7CGoogle%2520Chrome%3B138.0.7204.183&uamb=0&uam=&uap=Windows&uapv=19.0.0&uaw=0&fledge=1&data=event%3Dgtag.config
Requested by
Host: termsandconditions-5wn.pages.dev
URL: https://termsandconditions-5wn.pages.dev/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.20.157 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bx-in-f157.1e100.net
Software
/
Resource Hash
56351409e481ed955deaed718bbdc872da0f354c53091644f3b05e514c56b132

Request headers

Referer
https://termsandconditions-5wn.pages.dev/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
1577
content-type
text/html; charset=UTF-8
date
Sun, 30 Aug 2026 18:44:37 GMT
referrer-policy
no-referrer
GET
H2
404
934741711 Show response
td.doubleclick.net/td/rul/ Frame 51CD
2 KB
2 KB
551ms
155ms
Document
text/html
142.251.20.157
Google LLC
General
Full URL
https://td.doubleclick.net/td/rul/934741711?random=1753876666713&cv=11&fst=1753876666713&fmt=3&bg=ffffff&guid=ON&async=1&en=gtag.config&gtm=45be57s1v896649154z89195929391za200zb9195929391zd9195929391&gcd=13n3n3n3n5l1&dma=0&tag_exp=101509157~103116026~103200004~103233427~104684208~104684211~104948813~105087538~105087540~105103161~105103163~105124543~105124545&u_w=1920&u_h=1080&url=https%3A%2F%2Fthemeforest.net%2Fitem%2Fmarketica-marketplace-wordpress-theme%2F8988002%3Fsrsltid%3DAfmBOorwNEgJi-iQXu--3qzSatNlhXMhGjZ-gMFxbyMWP2LkJDdESL9b&ref=https%3A%2F%2Fwww.google.com%2F&hn=www.googleadservices.com&frm=0&tiba=Marketica%20-%20eCommerce%20and%20Marketplace%20-%20WooCommerce%20WordPress%20Theme%20by%20tokopress&npa=0&us_privacy=1---&pscdl=noapi&auid=786247872.1753876602&uaa=x86&uab=64&uafvl=Not)A%253BBrand%3B8.0.0.0%7CChromium%3B138.0.7204.183%7CGoogle%2520Chrome%3B138.0.7204.183&uamb=0&uam=&uap=Windows&uapv=19.0.0&uaw=0&fledge=1&data=event%3Dgtag.config
Requested by
Host: termsandconditions-5wn.pages.dev
URL: https://termsandconditions-5wn.pages.dev/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.20.157 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bx-in-f157.1e100.net
Software
/
Resource Hash
88aababcdb6b032aa4a3f9f6c913e05207ceda54a297aab7b82a80e475380d86

Request headers

Referer
https://termsandconditions-5wn.pages.dev/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
1577
content-type
text/html; charset=UTF-8
date
Sun, 30 Aug 2026 18:44:37 GMT
referrer-policy
no-referrer
POST
H2
200
index.php Show response
g.lzd-cdn.org/
2 B
277 B
118ms
41ms
XHR
application/json
3.9.176.51
Amazon.com
General
Full URL
https://g.lzd-cdn.org/index.php?cs=df9a8f72a88a997fddc883c771485ad8
Requested by
Host: g.lzd-cdn.org
URL: https://g.lzd-cdn.org/g/mtb/lib-mtop/2.5.1/polyfillB.js,mtb/lib-promise/3.1.3/mtop.js,mtb/lib-modules/1.1.4/pc.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
3.9.176.51 City of London, United Kingdom, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-3-9-176-51.eu-west-2.compute.amazonaws.com
Software
/
Resource Hash
44136fa355b3678a1146ad16f7e8649e94fb4fc21fe77e8310c060f61caaff8a

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
Content-Type
application/x-www-form-urlencoded
sec-ch-ua-mobile
?0

Response headers

cache-control
no-store
access-control-expose-headers
*
timing-allow-origin
*
accept-ch
Sec-CH-UA-Platform-Version, Sec-CH-UA-Model, Sec-CH-UA-Full-Version-List
etag
W/"2-vyGp6PvFo4RvsFtPoIWeCReyIC8"
access-control-allow-origin
*
content-length
2
date
Sun, 30 Aug 2026 18:44:37 GMT
content-type
application/json; charset=utf-8
GET
H2
200
googlelogo_color_150x54dp.png
www.google.com/images/branding/googlelogo/1x/ Frame AFF5
3 KB
4 KB
403ms
37ms
Image
image/png
142.251.157.119
Google LLC
General
Full URL
https://www.google.com/images/branding/googlelogo/1x/googlelogo_color_150x54dp.png
Requested by
Host: td.doubleclick.net
URL: https://td.doubleclick.net/td/rul/953691586?random=1753876666537&cv=11&fst=1753876666537&fmt=3&bg=ffffff&guid=ON&async=1&en=gtag.config&gtm=45be57s1z89195929391za200zb9195929391zd9195929391&gcd=13n3n3n3n5l1&dma=0&tag_exp=101509157~103116026~103200004~103233427~104684208~104684211~104948813~105103161~105103163~105124543~105124545&u_w=1920&u_h=1080&url=https%3A%2F%2Fthemeforest.net%2Fitem%2Fmarketica-marketplace-wordpress-theme%2F8988002%3Fsrsltid%3DAfmBOorwNEgJi-iQXu--3qzSatNlhXMhGjZ-gMFxbyMWP2LkJDdESL9b&ref=https%3A%2F%2Fwww.google.com%2F&hn=www.googleadservices.com&frm=0&tiba=Marketica%20-%20eCommerce%20and%20Marketplace%20-%20WooCommerce%20WordPress%20Theme%20by%20tokopress&npa=0&us_privacy=1---&pscdl=noapi&auid=786247872.1753876602&uaa=x86&uab=64&uafvl=Not)A%253BBrand%3B8.0.0.0%7CChromium%3B138.0.7204.183%7CGoogle%2520Chrome%3B138.0.7204.183&uamb=0&uam=&uap=Windows&uapv=19.0.0&uaw=0&fledge=1&data=event%3Dgtag.config
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.157.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
dbef5e5530003b7233e944856c23d1437902a2d3568cdfd2beaf2166e9ca9139
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://td.doubleclick.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
private, max-age=31536000
cross-origin-resource-policy
cross-origin
report-to
{"group":"static-on-bigtable","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/static-on-bigtable"}]}
x-content-type-options
nosniff
expires
Sun, 30 Aug 2026 18:44:37 GMT
accept-ranges
bytes
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cross-origin-opener-policy-report-only
same-origin; report-to="static-on-bigtable"
content-length
3170
date
Sun, 30 Aug 2026 18:44:37 GMT
x-xss-protection
0
content-type
image/png
last-modified
Tue, 22 Oct 2019 18:30:00 GMT
server
sffe
GET
H2
200
googlelogo_color_150x54dp.png
www.google.com/images/branding/googlelogo/1x/ Frame C949
3 KB
0
403ms
403ms
Image
image/png
142.251.157.119
Google LLC
General
Full URL
https://www.google.com/images/branding/googlelogo/1x/googlelogo_color_150x54dp.png
Requested by
Host: td.doubleclick.net
URL: https://td.doubleclick.net/td/rul/943617023?random=1753876666603&cv=11&fst=1753876666603&fmt=3&bg=ffffff&guid=ON&async=1&en=gtag.config&gtm=45be57s1v889115050z89195929391za200zb9195929391zd9195929391&gcd=13n3n3n3n5l1&dma=0&tag_exp=101509157~103116026~103200004~103233427~104684208~104684211~104948813~105103161~105103163~105124543~105124545&u_w=1920&u_h=1080&url=https%3A%2F%2Fthemeforest.net%2Fitem%2Fmarketica-marketplace-wordpress-theme%2F8988002%3Fsrsltid%3DAfmBOorwNEgJi-iQXu--3qzSatNlhXMhGjZ-gMFxbyMWP2LkJDdESL9b&ref=https%3A%2F%2Fwww.google.com%2F&hn=www.googleadservices.com&frm=0&tiba=Marketica%20-%20eCommerce%20and%20Marketplace%20-%20WooCommerce%20WordPress%20Theme%20by%20tokopress&npa=0&us_privacy=1---&pscdl=noapi&auid=786247872.1753876602&uaa=x86&uab=64&uafvl=Not)A%253BBrand%3B8.0.0.0%7CChromium%3B138.0.7204.183%7CGoogle%2520Chrome%3B138.0.7204.183&uamb=0&uam=&uap=Windows&uapv=19.0.0&uaw=0&fledge=1&data=event%3Dgtag.config
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.157.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
dbef5e5530003b7233e944856c23d1437902a2d3568cdfd2beaf2166e9ca9139
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://td.doubleclick.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
private, max-age=31536000
cross-origin-resource-policy
cross-origin
report-to
{"group":"static-on-bigtable","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/static-on-bigtable"}]}
x-content-type-options
nosniff
expires
Sun, 30 Aug 2026 18:44:37 GMT
accept-ranges
bytes
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cross-origin-opener-policy-report-only
same-origin; report-to="static-on-bigtable"
content-length
3170
date
Sun, 30 Aug 2026 18:44:37 GMT
x-xss-protection
0
content-type
image/png
last-modified
Tue, 22 Oct 2019 18:30:00 GMT
server
sffe
GET
H2
200
googlelogo_color_150x54dp.png
www.google.com/images/branding/googlelogo/1x/ Frame A3CC
3 KB
0
402ms
402ms
Image
image/png
142.251.157.119
Google LLC
General
Full URL
https://www.google.com/images/branding/googlelogo/1x/googlelogo_color_150x54dp.png
Requested by
Host: td.doubleclick.net
URL: https://td.doubleclick.net/td/rul/800411572?random=1753876666684&cv=11&fst=1753876666684&fmt=3&bg=ffffff&guid=ON&async=1&en=gtag.config&gtm=45be57s1v896649154z89195929391za200zb9195929391zd9195929391&gcd=13n3n3n3n5l1&dma=0&tag_exp=101509157~103116026~103200004~103233427~104684208~104684211~104948813~105087538~105087540~105103161~105103163~105124543~105124545&u_w=1920&u_h=1080&url=https%3A%2F%2Fthemeforest.net%2Fitem%2Fmarketica-marketplace-wordpress-theme%2F8988002%3Fsrsltid%3DAfmBOorwNEgJi-iQXu--3qzSatNlhXMhGjZ-gMFxbyMWP2LkJDdESL9b&ref=https%3A%2F%2Fwww.google.com%2F&hn=www.googleadservices.com&frm=0&tiba=Marketica%20-%20eCommerce%20and%20Marketplace%20-%20WooCommerce%20WordPress%20Theme%20by%20tokopress&npa=0&us_privacy=1---&pscdl=noapi&auid=786247872.1753876602&uaa=x86&uab=64&uafvl=Not)A%253BBrand%3B8.0.0.0%7CChromium%3B138.0.7204.183%7CGoogle%2520Chrome%3B138.0.7204.183&uamb=0&uam=&uap=Windows&uapv=19.0.0&uaw=0&fledge=1&data=event%3Dgtag.config
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.157.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
dbef5e5530003b7233e944856c23d1437902a2d3568cdfd2beaf2166e9ca9139
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://td.doubleclick.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
private, max-age=31536000
cross-origin-resource-policy
cross-origin
report-to
{"group":"static-on-bigtable","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/static-on-bigtable"}]}
x-content-type-options
nosniff
expires
Sun, 30 Aug 2026 18:44:37 GMT
accept-ranges
bytes
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cross-origin-opener-policy-report-only
same-origin; report-to="static-on-bigtable"
content-length
3170
date
Sun, 30 Aug 2026 18:44:37 GMT
x-xss-protection
0
content-type
image/png
last-modified
Tue, 22 Oct 2019 18:30:00 GMT
server
sffe
GET
H2
200
googlelogo_color_150x54dp.png
www.google.com/images/branding/googlelogo/1x/ Frame 51CD
3 KB
0
402ms
402ms
Image
image/png
142.251.157.119
Google LLC
General
Full URL
https://www.google.com/images/branding/googlelogo/1x/googlelogo_color_150x54dp.png
Requested by
Host: td.doubleclick.net
URL: https://td.doubleclick.net/td/rul/934741711?random=1753876666713&cv=11&fst=1753876666713&fmt=3&bg=ffffff&guid=ON&async=1&en=gtag.config&gtm=45be57s1v896649154z89195929391za200zb9195929391zd9195929391&gcd=13n3n3n3n5l1&dma=0&tag_exp=101509157~103116026~103200004~103233427~104684208~104684211~104948813~105087538~105087540~105103161~105103163~105124543~105124545&u_w=1920&u_h=1080&url=https%3A%2F%2Fthemeforest.net%2Fitem%2Fmarketica-marketplace-wordpress-theme%2F8988002%3Fsrsltid%3DAfmBOorwNEgJi-iQXu--3qzSatNlhXMhGjZ-gMFxbyMWP2LkJDdESL9b&ref=https%3A%2F%2Fwww.google.com%2F&hn=www.googleadservices.com&frm=0&tiba=Marketica%20-%20eCommerce%20and%20Marketplace%20-%20WooCommerce%20WordPress%20Theme%20by%20tokopress&npa=0&us_privacy=1---&pscdl=noapi&auid=786247872.1753876602&uaa=x86&uab=64&uafvl=Not)A%253BBrand%3B8.0.0.0%7CChromium%3B138.0.7204.183%7CGoogle%2520Chrome%3B138.0.7204.183&uamb=0&uam=&uap=Windows&uapv=19.0.0&uaw=0&fledge=1&data=event%3Dgtag.config
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.157.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
dbef5e5530003b7233e944856c23d1437902a2d3568cdfd2beaf2166e9ca9139
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://td.doubleclick.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
private, max-age=31536000
cross-origin-resource-policy
cross-origin
report-to
{"group":"static-on-bigtable","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/static-on-bigtable"}]}
x-content-type-options
nosniff
expires
Sun, 30 Aug 2026 18:44:37 GMT
accept-ranges
bytes
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cross-origin-opener-policy-report-only
same-origin; report-to="static-on-bigtable"
content-length
3170
date
Sun, 30 Aug 2026 18:44:37 GMT
x-xss-protection
0
content-type
image/png
last-modified
Tue, 22 Oct 2019 18:30:00 GMT
server
sffe
GET
H2
200
googlelogo_color_150x54dp.png
www.google.com/images/branding/googlelogo/1x/ Frame 35EB
3 KB
0
401ms
401ms
Image
image/png
142.251.157.119
Google LLC
General
Full URL
https://www.google.com/images/branding/googlelogo/1x/googlelogo_color_150x54dp.png
Requested by
Host: td.doubleclick.net
URL: https://td.doubleclick.net/td/rul/943617023?random=1753876666631&cv=11&fst=1753876666631&fmt=3&bg=ffffff&guid=ON&async=1&gtm=45be57s1v889115050z89195929391za200zb9195929391zd9195929391&gcd=13n3n3n3n5l1&dma=0&tag_exp=101509157~103116026~103200004~103233427~104684208~104684211~104948813~105103161~105103163~105124543~105124545&u_w=1920&u_h=1080&url=https%3A%2F%2Fthemeforest.net%2Fitem%2Fmarketica-marketplace-wordpress-theme%2F8988002%3Fsrsltid%3DAfmBOorwNEgJi-iQXu--3qzSatNlhXMhGjZ-gMFxbyMWP2LkJDdESL9b&ref=https%3A%2F%2Fwww.google.com%2F&hn=www.googleadservices.com&frm=0&tiba=Marketica%20-%20eCommerce%20and%20Marketplace%20-%20WooCommerce%20WordPress%20Theme%20by%20tokopress&did=dMWZhNz&gdid=dMWZhNz&npa=0&us_privacy=1---&pscdl=noapi&auid=786247872.1753876602&uaa=x86&uab=64&uafvl=Not)A%253BBrand%3B8.0.0.0%7CChromium%3B138.0.7204.183%7CGoogle%2520Chrome%3B138.0.7204.183&uamb=0&uam=&uap=Windows&uapv=19.0.0&uaw=0&fledge=1&_tu=Cg&data=ads_data_redaction%3Dfalse
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.157.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
dbef5e5530003b7233e944856c23d1437902a2d3568cdfd2beaf2166e9ca9139
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://td.doubleclick.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
private, max-age=31536000
cross-origin-resource-policy
cross-origin
report-to
{"group":"static-on-bigtable","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/static-on-bigtable"}]}
x-content-type-options
nosniff
expires
Sun, 30 Aug 2026 18:44:37 GMT
accept-ranges
bytes
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cross-origin-opener-policy-report-only
same-origin; report-to="static-on-bigtable"
content-length
3170
date
Sun, 30 Aug 2026 18:44:37 GMT
x-xss-protection
0
content-type
image/png
last-modified
Tue, 22 Oct 2019 18:30:00 GMT
server
sffe
GET
H2
200
js Show response
www.googletagmanager.com/gtag/
455 KB
157 KB
85ms
85ms
Script
application/javascript
142.251.20.97
Google LLC
General
Full URL
https://www.googletagmanager.com/gtag/js?id=G-9Z72VQCKY0&cx=c&gtm=4e68q1h1
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtm.js?id=GTM-W8KL5Q5
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.20.97 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bx-in-f97.1e100.net
Software
Google Tag Manager /
Resource Hash
446b8f0e9ec5fdedddfca2d40d6b0f6610fe91164535eaf20d740b6d8225cd93
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
private, max-age=900
content-encoding
zstd
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
expires
Sun, 30 Aug 2026 18:44:37 GMT
access-control-allow-origin
*
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
160628
date
Sun, 30 Aug 2026 18:44:37 GMT
x-xss-protection
0
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
server
Google Tag Manager
access-control-allow-headers
Cache-Control
GET
H2
200
js Show response
www.googletagmanager.com/gtag/
455 KB
157 KB
87ms
86ms
Script
application/javascript
142.251.20.97
Google LLC
General
Full URL
https://www.googletagmanager.com/gtag/js?id=AW-943617023&cx=c&gtm=4e68r0h2
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtm.js?id=GTM-KGCDGPL6
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.20.97 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bx-in-f97.1e100.net
Software
Google Tag Manager /
Resource Hash
21e15dae893fc96324c8fd2eebfec3c9fe5af7b74a9ddb16a099bcd8bbcdc779
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
zstd
expires
Sun, 30 Aug 2026 18:44:37 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sun, 30 Aug 2026 18:44:37 GMT
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
last-modified
Sun, 30 Aug 2026 18:00:00 GMT
access-control-allow-headers
Cache-Control
strict-transport-security
max-age=31536000; includeSubDomains
cache-control
private, max-age=900
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
access-control-allow-origin
*
content-length
160158
x-xss-protection
0
server
Google Tag Manager
GET
H2
200
js Show response
www.googletagmanager.com/gtag/
456 KB
157 KB
92ms
92ms
Script
application/javascript
142.251.20.97
Google LLC
General
Full URL
https://www.googletagmanager.com/gtag/js?id=AW-800411572&cx=c&gtm=4e68r0h2
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtm.js?id=GTM-KGCDGPL6
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.20.97 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bx-in-f97.1e100.net
Software
Google Tag Manager /
Resource Hash
d38ee2cdc33816c648c878bb024021caa761a5e7e1a9cf4e7cc6c67e09007a81
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
zstd
expires
Sun, 30 Aug 2026 18:44:37 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sun, 30 Aug 2026 18:44:37 GMT
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
last-modified
Sun, 30 Aug 2026 18:00:00 GMT
access-control-allow-headers
Cache-Control
strict-transport-security
max-age=31536000; includeSubDomains
cache-control
private, max-age=900
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
access-control-allow-origin
*
content-length
160283
x-xss-protection
0
server
Google Tag Manager
GET
H2
200
js Show response
www.googletagmanager.com/gtag/
414 KB
145 KB
93ms
93ms
Script
application/javascript
142.251.20.97
Google LLC
General
Full URL
https://www.googletagmanager.com/gtag/js?id=AW-953691586&cx=c&gtm=4e68r0h2
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtm.js?id=GTM-KGCDGPL6
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.20.97 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bx-in-f97.1e100.net
Software
Google Tag Manager /
Resource Hash
77df9eecbea5fc827dda1bae0bb097facc7985cf95e26082867cc97b87abc9ef
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
zstd
expires
Sun, 30 Aug 2026 18:44:37 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sun, 30 Aug 2026 18:44:37 GMT
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
last-modified
Sun, 30 Aug 2026 18:00:00 GMT
access-control-allow-headers
Cache-Control
strict-transport-security
max-age=31536000; includeSubDomains
cache-control
private, max-age=900
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
access-control-allow-origin
*
content-length
148568
x-xss-protection
0
server
Google Tag Manager
GET
H2
200
bat.js Show response
bat.bing.com/
54 KB
15 KB
37ms
37ms
Script
application/javascript
150.171.27.10
Microsoft Corpora...
General
Full URL
https://bat.bing.com/bat.js
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtm.js?id=GTM-KGCDGPL6
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
150.171.27.10 , United States, ASN8075 (MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation, US),
Reverse DNS
Software
/
Resource Hash
c7c9dcf09224020cb107b0e11f35f86424d927c1c967f9bcfcc3ec2979a6c7e1
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains; preload
cache-control
private,max-age=1800
content-encoding
gzip
etag
"08228456323dd1:0"
accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Mobile, Sec-CH-UA-Model, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
x-msedge-ref
Ref A: 7644FBF0875F49B78D8529C33121B238 Ref B: CPH011050219062 Ref C: 2026-08-30T18:44:37Z
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
x-cache
CONFIG_NOCACHE
content-length
15390
date
Sun, 30 Aug 2026 18:44:37 GMT
content-type
application/javascript
last-modified
Mon, 03 Aug 2026 16:15:16 GMT
vary
Accept-Encoding
POST
H2
200
collect
www.google.com/ccm/
0
0
403ms
37ms
Fetch
text/plain
142.251.151.119
Google LLC
General
Full URL
https://www.google.com/ccm/collect?rcb=13&frm=0&apvc=1&ae=g&auid=454011676.1788115478&dt=KEBAYA4D%20%3A%20Situs%20Gacor%20Hujan%20Scatter%20Mudah%20Jackpot%20Maxwin&en=page_view&dl=https%3A%2F%2Ftermsandconditions-5wn.pages.dev%2F&scrsrc=www.googletagmanager.com&rnd=949487753.1788115478&navt=n&npa=1&ep.ads_data_redaction=0&gtm=45He68r0h2v9195929391za200zd9195929391xea&gcd=13l3l3l2l1l1&dma_cps=a&dma=1&tag_exp=115616985~115938465~115938469~118897920~118897930~120385423~120763597&tft=1788115477699&tfd=1644&fmt=8
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtm.js?id=GTM-KGCDGPL6
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.151.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
/
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

POST
H3
204
collect
ad.doubleclick.net/ccm/s/
0
0
137ms
60ms
Fetch
text/html
142.251.13.149
Google LLC
General
Full URL
https://ad.doubleclick.net/ccm/s/collect?auid=454011676.1788115478&gtm=45He68r0h2v9195929391za200zd9195929391xea&fmt=8
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtm.js?id=GTM-KGCDGPL6
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.13.149 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
wt-in-f149.1e100.net
Software
/
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

GET
H2
200
16005611.js Show response
bat.bing.com/p/action/
397 B
0
0ms
0ms
Script
application/javascript
150.171.27.10
Microsoft Corpora...
General
Full URL
https://bat.bing.com/p/action/16005611.js
Requested by
Host: bat.bing.com
URL: https://bat.bing.com/bat.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
150.171.27.10 , United States, ASN8075 (MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation, US),
Reverse DNS
Software
/
Resource Hash
e36cd50b6c1410f6efe1091b16f6d846e8ac00beb26d5ea265b401a2fc40360a

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
private,max-age=1800
content-encoding
br
accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Mobile, Sec-CH-UA-Model, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
x-msedge-ref
Ref A: B89F50C58AFF48009675F95C0797A3A7 Ref B: CPH011050219062 Ref C: 2026-08-30T18:44:37Z
cross-origin-resource-policy
cross-origin
x-cache
CONFIG_NOCACHE
date
Sun, 30 Aug 2026 18:44:36 GMT
content-type
application/javascript; charset=utf-8
vary
Accept-Encoding
GET
H2
204
0
bat.bing.com/action/
0
123 B
37ms
37ms
Image
text/plain
150.171.27.10
Microsoft Corpora...
General
Full URL
https://bat.bing.com/action/0?ti=16005611&tm=gtm002&Ver=2&mid=93ae546d-dd6d-4e8a-986b-d47142f40d7c&bo=1&sid=da340210a4a211f19fdf9d680bf1c9df&vid=da33f8a0a4a211f1955b5b0dd96e3fe2&vids=1&msclkid=N&pi=918639831&lg=da-DK&sw=1600&sh=1200&sc=24&tl=KEBAYA4D%20%3A%20Situs%20Gacor%20Hujan%20Scatter%20Mudah%20Jackpot%20Maxwin&p=https%3A%2F%2Ftermsandconditions-5wn.pages.dev%2F&r=&lt=936&evt=pageLoad&sv=2&cdb=AQAQ&rn=801481
Requested by
Host: termsandconditions-5wn.pages.dev
URL: https://termsandconditions-5wn.pages.dev/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
150.171.27.10 , United States, ASN8075 (MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation, US),
Reverse DNS
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains; preload
cache-control
no-cache, must-revalidate
pragma
no-cache
accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Mobile, Sec-CH-UA-Model, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
x-msedge-ref
Ref A: D3D1200C81B74CF3B20E03A661D55692 Ref B: CPH011050219062 Ref C: 2026-08-30T18:44:37Z
expires
Fri, 01 Jan 1990 00:00:00 GMT
access-control-allow-origin
*
x-cache
CONFIG_NOCACHE
date
Sun, 30 Aug 2026 18:44:37 GMT
POST
H2
204
collect
region1.google-analytics.com/g/
0
0
409ms
39ms
Fetch
text/plain
216.239.32.36
Google LLC
General
Full URL
https://region1.google-analytics.com/g/collect?v=2&tid=G-9Z72VQCKY0&gtm=45je68q1h1v9119618425z89117991082za20gzb9117991082zd9117991082&_p=1788115476762&gcd=13l3lPl2l1l1&npa=1&dma_cps=a&dma=1&cid=68839237.1788115478&frm=0&ngs=1&pscdl=noapi&rcb=11&sr=1600x1200&uaa=x86&uab=64&uafvl=Chromium%3B152.0.0.0%7CGoogle%2520Chrome%3B152.0.0.0%7CNot%253FA_Brand%3B24.0.0.0&uam=&uamb=0&uap=Linux&uapv=&uaw=0&ul=da-dk&_s=1&tag_exp=115938465~115938469~118897920~118897930~120213116~120385422~120412527&dl=https%3A%2F%2Ftermsandconditions-5wn.pages.dev%2F&dr=&dt=KEBAYA4D%20%3A%20Situs%20Gacor%20Hujan%20Scatter%20Mudah%20Jackpot%20Maxwin&sid=1788115477&sct=1&seg=0&en=page_view&_fv=1&_nsi=1&_ss=1&ep.app_name=marketplace&ep.app_env=production&ep.app_version=f7d8b3d494288b34cb00105ee5d230d68b0ccca7&ep.page_type=item&epn.custom_timestamp=1788115476948&ep.event_type=user&ep.url_snippet_start=&ep.url_snippet_end=&tfd=1826
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtag/js?id=G-9Z72VQCKY0&cx=c&gtm=4e68q1h1
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
216.239.32.36 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
Golfe2 /
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, no-store, must-revalidate
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
content-security-policy-report-only
script-src 'none'; form-action 'none'; frame-src 'none'; report-uri https://csp.withgoogle.com/csp/scaffolding/ascnsrsggc:139:0
report-to
{"group":"ascnsrsggc:139:0","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/scaffolding/ascnsrsggc:139:0"}],}
expires
Fri, 01 Jan 1990 00:00:00 GMT
access-control-allow-origin
https://termsandconditions-5wn.pages.dev
cross-origin-opener-policy-report-only
same-origin; report-to=ascnsrsggc:139:0
content-length
0
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sun, 30 Aug 2026 18:44:38 GMT
content-type
text/plain
server
Golfe2
POST
H2
200
collect
www.google.com/ccm/
0
0
185ms
42ms
Fetch
text/plain
142.251.151.119
Google LLC
General
Full URL
https://www.google.com/ccm/collect?rcb=3&frm=0&apvc=0&auid=454011676.1788115478&dt=KEBAYA4D%20%3A%20Situs%20Gacor%20Hujan%20Scatter%20Mudah%20Jackpot%20Maxwin&tid=AW-953691586&en=page_view&dl=https%3A%2F%2Ftermsandconditions-5wn.pages.dev%2F&scrsrc=www.googletagmanager.com&rnd=949487753.1788115478&navt=n&npa=1&gtm=45be68r0h2z89195929391za20gzb9195929391zd9195929391xec&gcd=13l3l3l2l1l1&dma_cps=a&dma=1&tag_exp=115938465~115938468~118897920~118897930~120385423~120763597&tft=1788115477923&tfd=1867&tids=AW-953691586&fmt=8
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtag/js?id=AW-953691586&cx=c&gtm=4e68r0h2
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.151.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
/
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

POST
H2
200
collect
www.google.com/ccm/
0
0
143ms
40ms
Fetch
text/plain
142.251.151.119
Google LLC
General
Full URL
https://www.google.com/ccm/collect?rcb=11&frm=0&apvc=0&auid=454011676.1788115478&dt=KEBAYA4D%20%3A%20Situs%20Gacor%20Hujan%20Scatter%20Mudah%20Jackpot%20Maxwin&tid=AW-800411572&en=page_view&dl=https%3A%2F%2Ftermsandconditions-5wn.pages.dev%2F&scrsrc=www.googletagmanager.com&rnd=949487753.1788115478&navt=n&npa=1&gtm=45be68r0h2v896649154z89195929391za20gzb9195929391zd9195929391xec&gcd=13l3l3l2l1l1&dma_cps=a&dma=1&tag_exp=115938465~115938468~118897920~118897930~119381662~119793973~120385423~120412528&tft=1788115477963&tfd=1908&tids=AW-800411572~AW-934741711&fmt=8
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtag/js?id=AW-800411572&cx=c&gtm=4e68r0h2
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.151.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
/
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

POST
H2
200
collect
www.google.com/ccm/
0
0
103ms
41ms
Fetch
text/plain
142.251.151.119
Google LLC
General
Full URL
https://www.google.com/ccm/collect?rcb=9&frm=0&apvc=0&auid=454011676.1788115478&dt=KEBAYA4D%20%3A%20Situs%20Gacor%20Hujan%20Scatter%20Mudah%20Jackpot%20Maxwin&tid=AW-943617023&en=page_view&dl=https%3A%2F%2Ftermsandconditions-5wn.pages.dev%2F&scrsrc=www.googletagmanager.com&rnd=949487753.1788115478&navt=n&npa=1&gtm=45be68r0h2v889115050z89195929391za20gzb9195929391zd9195929391xec&gcd=13l3lPl2l1l1&dma_cps=a&dma=1&tag_exp=115938465~115938469~118897920~118897930~120385423&tft=1788115478003&tfd=1948&tids=AW-943617023&fmt=8
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtag/js?id=AW-943617023&cx=c&gtm=4e68r0h2
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.151.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
/
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

POST
H2
200
collect
www.google.com/ccm/
0
0
102ms
40ms
Fetch
text/plain
142.251.151.119
Google LLC
General
Full URL
https://www.google.com/ccm/collect?rcb=9&frm=0&apvc=0&ae=g&auid=454011676.1788115478&dt=KEBAYA4D%20%3A%20Situs%20Gacor%20Hujan%20Scatter%20Mudah%20Jackpot%20Maxwin&tid=AW-943617023&dl=https%3A%2F%2Ftermsandconditions-5wn.pages.dev%2F&scrsrc=www.googletagmanager.com&rnd=949487753.1788115478&navt=n&npa=1&_tu=CA&gtm=45be68r0h2v889115050z89195929391za20gzb9195929391zd9195929391xea&gcd=13l3lPl2l1l1&dma_cps=a&dma=1&tag_exp=115938465~115938469~118897920~118897930~120385423&tft=1788115478004&tfd=1949&tids=AW-943617023&fmt=8
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtag/js?id=AW-943617023&cx=c&gtm=4e68r0h2
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.151.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
/
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

GET
H2
401
images_-_2025-09-07T215509.531_iovr71.jpg
res.cloudinary.com/db5uodec1/image/upload/v1757256934/
0
117 B
19ms
19ms
Other
image/gif
151.101.193.137
Fastly
General
Full URL
https://res.cloudinary.com/db5uodec1/image/upload/v1757256934/images_-_2025-09-07T215509.531_iovr71.jpg
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.137 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
Cloudinary /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=604800

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=604800
cache-control
private, no-transform, max-age=0, no-cache
timing-allow-origin
*
access-control-expose-headers
Content-Length,Content-Disposition,Server-Timing,X-Cld-Error
pragma
no-cache
content-transfer-encoding
binary
accept-ranges
bytes
x-cld-error
cloud_name db5uodec1 is disabled
server-timing
cld-fastly;mitm=p;dur=1;cpu=0;start=2026-08-30T18:44:38.017Z;desc=hit,rtt;dur=22
content-length
0
access-control-allow-origin
*
date
Sun, 30 Aug 2026 18:44:38 GMT
content-disposition
inline
content-type
image/gif
server
Cloudinary
POST
H2
204
collect
region1.google-analytics.com/g/
0
0
41ms
40ms
Fetch
text/plain
216.239.32.36
Google LLC
General
Full URL
https://region1.google-analytics.com/g/collect?v=2&tid=G-9Z72VQCKY0&gtm=45je68q1h1v9119618425z89117991082za20gzb9117991082zd9117991082&_p=1788115476762&gcd=13l3lPl2l1l1&npa=1&dma_cps=a&dma=1&_eu=IAAAAAQ&cid=68839237.1788115478&frm=0&ngs=1&pscdl=noapi&rcb=11&sr=1600x1200&uaa=x86&uab=64&uafvl=Chromium%3B152.0.0.0%7CGoogle%2520Chrome%3B152.0.0.0%7CNot%253FA_Brand%3B24.0.0.0&uam=&uamb=0&uap=Linux&uapv=&uaw=0&ul=da-dk&_s=2&tag_exp=115938465~115938469~118897920~118897930~120213116~120385422~120412527&cu=usd&dl=https%3A%2F%2Ftermsandconditions-5wn.pages.dev%2F&dr=&dt=KEBAYA4D%20%3A%20Situs%20Gacor%20Hujan%20Scatter%20Mudah%20Jackpot%20Maxwin&sid=1788115477&sct=1&seg=0&en=view_item&pr1=afthemeforest~id8988002~nmkebaya4d%20%3A%20situs%20gacor%20hujan%20scatter%20mudah%20jackpot%20maxwin~brtokopress~cawordpress~c2ecommerce~c3woocommerce~pr37~qt1~k0item_add_on~v0bundle_6month~varegular&ep.value=37&ep.app_name=marketplace&ep.app_env=production&ep.app_version=f7d8b3d494288b34cb00105ee5d230d68b0ccca7&ep.page_type=item&epn.custom_timestamp=1788115476949&ep.event_type=user&ep.url_snippet_start=&ep.url_snippet_end=&_et=2&tfd=6829
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtag/js?id=G-9Z72VQCKY0&cx=c&gtm=4e68q1h1
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
216.239.32.36 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
Golfe2 /
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://termsandconditions-5wn.pages.dev/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, no-store, must-revalidate
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
content-security-policy-report-only
script-src 'none'; form-action 'none'; frame-src 'none'; report-uri https://csp.withgoogle.com/csp/scaffolding/ascnsrsggc:139:0
report-to
{"group":"ascnsrsggc:139:0","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/scaffolding/ascnsrsggc:139:0"}],}
expires
Fri, 01 Jan 1990 00:00:00 GMT
access-control-allow-origin
https://termsandconditions-5wn.pages.dev
cross-origin-opener-policy-report-only
same-origin; report-to=ascnsrsggc:139:0
content-length
0
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sun, 30 Aug 2026 18:44:42 GMT
content-type
text/plain
server
Golfe2

Failed requests

These URLs were requested, but there was no response received. You will also see them in the list above.

Domain
wptheme.cloud
URL
https://wptheme.cloud/wp-includes/wp-elements/wp-emoji-release-version.2.7.js

Verdicts & Comments Add Verdict or Comment

29 JavaScript Window variables Go Pro

Only in urlscan Pro

Inspect and pivot on JavaScript variables, identifiers, and other key site metadata data with urlscan Pro. Reveal and search on client-side frameworks, runtime variables, and custom values.
Click for more information
Free trials of urlscan Pro are available.

These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.

object| 0 object| 1 object| 2 object| 3 object| 4 object| 5 object| 6 object| 7 object| DATADOG_CONFIG string| rollbarEnvironment string| codeVersion object| dataLayer string| container_env_param string| gtmId object| html5 object| Modernizr object| GtmMeasurements function| trimGacUaCookies function| trimGaSessionCookies object| datadog_attributes object| google_tag_manager object| google_tag_data function| gtag function| UET function| UET_init function| UET_push object| ueto_1e271fd20c object| uetq object| gaGlobal

7 Cookies Go Pro

Only in urlscan Pro

Review, search, and pivot on browser cookies and persistence site data to see how a site tracks users and keeps sessions alive across visits.
Click for more information
Free trials of urlscan Pro are available.

Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.

Domain/Path Expires Name / Value
.envatousercontent.com/ 1970-01-21
16:41:57
Name: __cf_bm
Value: Mxu2ZaOw0Zlo2RApza4LKbGC0n4KssFYEzsnfBCqLi8-1788115476.6155112-1.0.1.1-msu0UkjI6djy38S2gRjlB_E6xR2PS0BRjKblBsxsMt1DlwBEklCuyBIfl.WC3Cte.mlATRMxVI6B7bt4DvCwxq9aEacDVAPmCKAS2bXxa8ltIgqXSJdNR2OFF92uJ_BV
.bing.com/ 1970-01-22
02:03:31
Name: MUID
Value: 305B67143CDA62D117D570D13D4063AD
.termsandconditions-5wn.pages.dev/ 1970-01-21
18:51:31
Name: _gcl_au
Value: 1.1.454011676.1788115478
.termsandconditions-5wn.pages.dev/ 1970-01-21
16:43:21
Name: _uetsid
Value: da340210a4a211f19fdf9d680bf1c9df
.termsandconditions-5wn.pages.dev/ 1970-01-22
02:03:31
Name: _uetvid
Value: da33f8a0a4a211f1955b5b0dd96e3fe2
.termsandconditions-5wn.pages.dev/ 1970-01-22
02:17:55
Name: _ga
Value: GA1.1.68839237.1788115478
.termsandconditions-5wn.pages.dev/ 1970-01-22
02:17:55
Name: _ga_9Z72VQCKY0
Value: GS2.1.s1788115477$o1$g0$t1788115477$j60$l0$h0

12 Console Messages

A page may trigger messages to the console to be logged. These are often error messages about being unable to load a resource or execute a piece of JavaScript. Sometimes they also provide insight into the technology behind a website.

Source Level URL
Text
network error URL: https://wptheme.cloud/wp-includes/wp-elements/wp-emoji-release-version.2.7.js
Message:
Failed to load resource: net::ERR_BLOCKED_BY_RESPONSE.NotSameOrigin
network error URL: https://res.cloudinary.com/db5uodec1/image/upload/v1758211590/bKtCv_wd5nyx.png
Message:
Failed to load resource: the server responded with a status of 401 ()
network error URL: https://res.cloudinary.com/db5uodec1/image/upload/v1758211590/bKtCv_wd5nyx.png
Message:
Failed to load resource: the server responded with a status of 401 ()
network error URL: https://td.doubleclick.net/td/rul/953691586?random=1753876666537&cv=11&fst=1753876666537&fmt=3&bg=ffffff&guid=ON&async=1&en=gtag.config&gtm=45be57s1z89195929391za200zb9195929391zd9195929391&gcd=13n3n3n3n5l1&dma=0&tag_exp=101509157~103116026~103200004~103233427~104684208~104684211~104948813~105103161~105103163~105124543~105124545&u_w=1920&u_h=1080&url=https%3A%2F%2Fthemeforest.net%2Fitem%2Fmarketica-marketplace-wordpress-theme%2F8988002%3Fsrsltid%3DAfmBOorwNEgJi-iQXu--3qzSatNlhXMhGjZ-gMFxbyMWP2LkJDdESL9b&ref=https%3A%2F%2Fwww.google.com%2F&hn=www.googleadservices.com&frm=0&tiba=Marketica%20-%20eCommerce%20and%20Marketplace%20-%20WooCommerce%20WordPress%20Theme%20by%20tokopress&npa=0&us_privacy=1---&pscdl=noapi&auid=786247872.1753876602&uaa=x86&uab=64&uafvl=Not)A%253BBrand%3B8.0.0.0%7CChromium%3B138.0.7204.183%7CGoogle%2520Chrome%3B138.0.7204.183&uamb=0&uam=&uap=Windows&uapv=19.0.0&uaw=0&fledge=1&data=event%3Dgtag.config
Message:
Failed to load resource: the server responded with a status of 404 ()
network error URL: https://td.doubleclick.net/td/rul/943617023?random=1753876666603&cv=11&fst=1753876666603&fmt=3&bg=ffffff&guid=ON&async=1&en=gtag.config&gtm=45be57s1v889115050z89195929391za200zb9195929391zd9195929391&gcd=13n3n3n3n5l1&dma=0&tag_exp=101509157~103116026~103200004~103233427~104684208~104684211~104948813~105103161~105103163~105124543~105124545&u_w=1920&u_h=1080&url=https%3A%2F%2Fthemeforest.net%2Fitem%2Fmarketica-marketplace-wordpress-theme%2F8988002%3Fsrsltid%3DAfmBOorwNEgJi-iQXu--3qzSatNlhXMhGjZ-gMFxbyMWP2LkJDdESL9b&ref=https%3A%2F%2Fwww.google.com%2F&hn=www.googleadservices.com&frm=0&tiba=Marketica%20-%20eCommerce%20and%20Marketplace%20-%20WooCommerce%20WordPress%20Theme%20by%20tokopress&npa=0&us_privacy=1---&pscdl=noapi&auid=786247872.1753876602&uaa=x86&uab=64&uafvl=Not)A%253BBrand%3B8.0.0.0%7CChromium%3B138.0.7204.183%7CGoogle%2520Chrome%3B138.0.7204.183&uamb=0&uam=&uap=Windows&uapv=19.0.0&uaw=0&fledge=1&data=event%3Dgtag.config
Message:
Failed to load resource: the server responded with a status of 404 ()
network error URL: https://td.doubleclick.net/td/rul/800411572?random=1753876666684&cv=11&fst=1753876666684&fmt=3&bg=ffffff&guid=ON&async=1&en=gtag.config&gtm=45be57s1v896649154z89195929391za200zb9195929391zd9195929391&gcd=13n3n3n3n5l1&dma=0&tag_exp=101509157~103116026~103200004~103233427~104684208~104684211~104948813~105087538~105087540~105103161~105103163~105124543~105124545&u_w=1920&u_h=1080&url=https%3A%2F%2Fthemeforest.net%2Fitem%2Fmarketica-marketplace-wordpress-theme%2F8988002%3Fsrsltid%3DAfmBOorwNEgJi-iQXu--3qzSatNlhXMhGjZ-gMFxbyMWP2LkJDdESL9b&ref=https%3A%2F%2Fwww.google.com%2F&hn=www.googleadservices.com&frm=0&tiba=Marketica%20-%20eCommerce%20and%20Marketplace%20-%20WooCommerce%20WordPress%20Theme%20by%20tokopress&npa=0&us_privacy=1---&pscdl=noapi&auid=786247872.1753876602&uaa=x86&uab=64&uafvl=Not)A%253BBrand%3B8.0.0.0%7CChromium%3B138.0.7204.183%7CGoogle%2520Chrome%3B138.0.7204.183&uamb=0&uam=&uap=Windows&uapv=19.0.0&uaw=0&fledge=1&data=event%3Dgtag.config
Message:
Failed to load resource: the server responded with a status of 404 ()
network error URL: https://td.doubleclick.net/td/rul/934741711?random=1753876666713&cv=11&fst=1753876666713&fmt=3&bg=ffffff&guid=ON&async=1&en=gtag.config&gtm=45be57s1v896649154z89195929391za200zb9195929391zd9195929391&gcd=13n3n3n3n5l1&dma=0&tag_exp=101509157~103116026~103200004~103233427~104684208~104684211~104948813~105087538~105087540~105103161~105103163~105124543~105124545&u_w=1920&u_h=1080&url=https%3A%2F%2Fthemeforest.net%2Fitem%2Fmarketica-marketplace-wordpress-theme%2F8988002%3Fsrsltid%3DAfmBOorwNEgJi-iQXu--3qzSatNlhXMhGjZ-gMFxbyMWP2LkJDdESL9b&ref=https%3A%2F%2Fwww.google.com%2F&hn=www.googleadservices.com&frm=0&tiba=Marketica%20-%20eCommerce%20and%20Marketplace%20-%20WooCommerce%20WordPress%20Theme%20by%20tokopress&npa=0&us_privacy=1---&pscdl=noapi&auid=786247872.1753876602&uaa=x86&uab=64&uafvl=Not)A%253BBrand%3B8.0.0.0%7CChromium%3B138.0.7204.183%7CGoogle%2520Chrome%3B138.0.7204.183&uamb=0&uam=&uap=Windows&uapv=19.0.0&uaw=0&fledge=1&data=event%3Dgtag.config
Message:
Failed to load resource: the server responded with a status of 404 ()
network error URL: https://td.doubleclick.net/td/rul/943617023?random=1753876666631&cv=11&fst=1753876666631&fmt=3&bg=ffffff&guid=ON&async=1&gtm=45be57s1v889115050z89195929391za200zb9195929391zd9195929391&gcd=13n3n3n3n5l1&dma=0&tag_exp=101509157~103116026~103200004~103233427~104684208~104684211~104948813~105103161~105103163~105124543~105124545&u_w=1920&u_h=1080&url=https%3A%2F%2Fthemeforest.net%2Fitem%2Fmarketica-marketplace-wordpress-theme%2F8988002%3Fsrsltid%3DAfmBOorwNEgJi-iQXu--3qzSatNlhXMhGjZ-gMFxbyMWP2LkJDdESL9b&ref=https%3A%2F%2Fwww.google.com%2F&hn=www.googleadservices.com&frm=0&tiba=Marketica%20-%20eCommerce%20and%20Marketplace%20-%20WooCommerce%20WordPress%20Theme%20by%20tokopress&did=dMWZhNz&gdid=dMWZhNz&npa=0&us_privacy=1---&pscdl=noapi&auid=786247872.1753876602&uaa=x86&uab=64&uafvl=Not)A%253BBrand%3B8.0.0.0%7CChromium%3B138.0.7204.183%7CGoogle%2520Chrome%3B138.0.7204.183&uamb=0&uam=&uap=Windows&uapv=19.0.0&uaw=0&fledge=1&_tu=Cg&data=ads_data_redaction%3Dfalse
Message:
Failed to load resource: the server responded with a status of 404 ()
network error URL: https://res.cloudinary.com/db5uodec1/image/upload/v1757256934/images_-_2025-09-07T215509.531_iovr71.jpg
Message:
Failed to load resource: the server responded with a status of 401 ()
javascript warning URL: https://termsandconditions-5wn.pages.dev/
Message:
The resource https://market-resized.envatousercontent.com/themeforest.net/files/344043819/MARKETICA_PREVIEW/00-marketica-preview-sale37.__large_preview.jpg?auto=format&q=94&cf_fit=crop&gravity=top&h=8000&w=590&s=cc700268e0638344373c64d90d02d184c75d7defef1511b43f3ecf3627a3f2d4 was preloaded using link preload but not used within a few seconds from the window's load event. Please make sure it has an appropriate `as` value and it is preloaded intentionally.
javascript warning URL: https://termsandconditions-5wn.pages.dev/
Message:
The resource https://public-assets.envato-static.com/assets/generated_sprites/common-5af54247f3a645893af51456ee4c483f6530608e9c15ca4a8ac5a6e994d9a340.png was preloaded using link preload but not used within a few seconds from the window's load event. Please make sure it has an appropriate `as` value and it is preloaded intentionally.
javascript warning URL: https://termsandconditions-5wn.pages.dev/
Message:
The resource https://public-assets.envato-static.com/assets/generated_sprites/logos-20f56d7ae7a08da2c6698db678490c591ce302aedb1fcd05d3ad1e1484d3caf9.png was preloaded using link preload but not used within a few seconds from the window's load event. Please make sure it has an appropriate `as` value and it is preloaded intentionally.

Security Headers

This page lists any security headers set by the main page. If you want to understand what these mean and how to use them, head on over to this page

Header Value
X-Content-Type-Options nosniff

Indicators

This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.

ad.doubleclick.net
bat.bing.com
consentcdn.cookiebot.com
g.lzd-cdn.org
i.pinimg.com
imgsct.cookiebot.com
market-resized.envatousercontent.com
public-assets.envato-static.com
region1.google-analytics.com
res.cloudinary.com
td.doubleclick.net
termsandconditions-5wn.pages.dev
wptheme.cloud
www.google.com
www.googletagmanager.com
wptheme.cloud
104.81.4.96
142.251.13.149
142.251.151.119
142.251.157.119
142.251.20.157
142.251.20.97
150.171.27.10
151.101.192.84
151.101.193.137
172.64.146.183
188.114.96.3
216.239.32.36
23.215.20.211
3.9.176.51
65.8.131.2
071b9668932fc901d7f779ee9bfd9b05a30bcde960751a66ff8b586d9d051fc2
14f8bc60470b39265fe5c01e92035209bd04b91cd7da99d59ca3ccd9de5eac62
21e15dae893fc96324c8fd2eebfec3c9fe5af7b74a9ddb16a099bcd8bbcdc779
29a010cf21230d20587e431ec9153c928fee096d9bf6740815c96fa93ddc0d21
3314bbeb196f5f1858b98256fe14b1bbe632f6b4077d311139e8173f3cfc2945
44136fa355b3678a1146ad16f7e8649e94fb4fc21fe77e8310c060f61caaff8a
446b8f0e9ec5fdedddfca2d40d6b0f6610fe91164535eaf20d740b6d8225cd93
5248900f1317a0f8cab40d0a15332adc13d7906bb0df4ef1c33c4438b87ae335
56351409e481ed955deaed718bbdc872da0f354c53091644f3b05e514c56b132
60360733662f006fbc87df4a1e92df08edf0785dc3e33130fc2b7ac0e3d7fbec
6328e6b9e5c4f7ac64d124dde5d2b9412efdf0988ea4fb8bc156d501ff44216a
6902a46cd3be583fdda26df9df6a07d8c4d2fbecc4bfaa685c1884e396122eb2
6a2810521190291abcf97c153fee9ffe8846cb04c087f23e7d1eb56b5db836fd
6adc3d4c1056996e4e8b765a62604c78b1f867cceb3b15d0b9bedb7c4857f992
6f8a015ab6d9602102f6c4dde38bf1a128f2647f20b76023c4793c2d3d86e57c
6fa14e1612d83cbf85d02a06ca88d47e8c90c71545d27b292174ddd0073b4259
738e5435f2d18427d291a0d6289eee0ebbc87b596d6003919f255760ac293104
77df9eecbea5fc827dda1bae0bb097facc7985cf95e26082867cc97b87abc9ef
88aababcdb6b032aa4a3f9f6c913e05207ceda54a297aab7b82a80e475380d86
89c24d697618dd08e5585cc2dc210afe6b8d89e547453a05e19b6a7c91fe73b6
8adad9ee9ef1b7fa392ee2d5a769d3f43a9462bed8e3d8be57c02faa332bc244
8ba45b7315225b2246e1b7408f1d742f195bfc1713b384af8b65a04c1f8e5454
8dd050ef03bd01da25a5b5d25e02940fce69bd9accd49e3baae50d46a532d70c
9d22b4007cc21a935e65245bd8090214db4fc3eed3aecdd1d455cd154f78612a
c401d80a6dd4c3266b32934928ed11ddd1d06939c6758bfd837416eb0ee3b58a
c42844045ae09380561d14fd2e5ee08454fd46b9d3f6ebeea4a19c6e7a7fe2ca
c7c9dcf09224020cb107b0e11f35f86424d927c1c967f9bcfcc3ec2979a6c7e1
d38ee2cdc33816c648c878bb024021caa761a5e7e1a9cf4e7cc6c67e09007a81
dbef5e5530003b7233e944856c23d1437902a2d3568cdfd2beaf2166e9ca9139
dbf8c90e7cdc155dfc29a7f760e9efafa41e8a3a5a19c3320b995687d6ddff51
e36cd50b6c1410f6efe1091b16f6d846e8ac00beb26d5ea265b401a2fc40360a
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
ea3a60ea39171409e4f531bab81dc0a0f23d5ab62c5bbc2160599b766c5803dd