
laojiacn.com
139.162.11.114
Malicious Activity!
Public Scan
Open in
urlscan Pro
https://laojiacn.com/ 6yr old
Submission: On August 31 via api (August 31st 2026, 6:09:01 pm UTC) from BE — Scanned from SG Go Pro
Only in urlscan Pro
- Select different country locations for Private Scans.
- Use a global network of additional scanning locations and residential IPs for scanning.
- Interact with pages while you are scanning them.
- Download files from remote websites.
- Scan websites on the Tor Network.
Summary
TLS certificate: Issued by YR1 on July 13th 2026. Valid for: 3mo.
This is the only time laojiacn.com was scanned on urlscan.io!
urlscan.io Verdict: Potentially Malicious
Domain & IP information
| IP Address | AS Autonomous System | ||
|---|---|---|---|
| 35 | 139.162.11.114 139.162.11.114 | 63949 (AKAMAI-LI...) (AKAMAI-LINODE-AP - Akamai Connected Cloud) | |
| 1 | 172.247.46.243 172.247.46.243 | 40065 (CNSERVERS) (CNSERVERS - CNSERVERS LLC) | |
| 1 | 172.67.194.33 172.67.194.33 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 14.215.182.140 14.215.182.140 | 4134 (CHINANET-...) (CHINANET-BACKBONE - No.31) | |
| 2 | 43.169.32.101 43.169.32.101 | 139341 (ACE-AS-AP) (ACE-AS-AP - ACE) | |
| 1 | 36.248.16.48 36.248.16.48 | 4837 (CHINA169-...) (CHINA169-Backbone - CHINA UNICOM China169 Backbone) | |
| 1 | 98.98.225.192 98.98.225.192 | 21859 (ZEN-ECN) (ZEN-ECN - Zenlayer Inc) | |
| 42 | 7 |
ASN63949 (AKAMAI-LINODE-AP - Akamai Connected Cloud, SG)
PTR: 139-162-11-114.ip.linodeusercontent.com
| laojiacn.com 6yr old | |
| img.365ty.top 1yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| img.thethsdnadagvx.com 4yr old |
ASN4134 (CHINANET-BACKBONE - No.31,Jin-rong Street, CN)
| hm.baidu.com 14yr old |
ASN4837 (CHINA169-Backbone - CHINA UNICOM China169 Backbone, CN)
| zz.bdstatic.com 10yr old |
| Apex Domain Subdomains |
Transfer | |
|---|---|---|
| 23 |
laojiacn.com
laojiacn.com 6yr old |
742 KB |
| 12 |
365ty.top
img.365ty.top 1yr old |
507 KB |
| 2 |
aizhantj.com
node92.aizhantj.com — Cisco Umbrella Rank: 366104 1yr old |
13 KB |
| 2 |
baidu.com
hm.baidu.com — Cisco Umbrella Rank: 12387 14yr old sp0.baidu.com — Cisco Umbrella Rank: 44272 10yr old |
752 B |
| 1 |
bdstatic.com
zz.bdstatic.com — Cisco Umbrella Rank: 77980 10yr old |
562 B |
| 1 |
thethsdnadagvx.com
img.thethsdnadagvx.com — Cisco Umbrella Rank: 620755 4yr old |
39 KB |
| 1 |
8169idc.com
365ty.8169idc.com 3mo old |
14 KB |
| 42 | 7 |
| Domain | Requested by | |
|---|---|---|
| 23 | laojiacn.com |
laojiacn.com
|
| 12 | img.365ty.top |
laojiacn.com
|
| 2 | node92.aizhantj.com |
laojiacn.com
node92.aizhantj.com |
| 1 | sp0.baidu.com |
laojiacn.com
|
| 1 | zz.bdstatic.com |
laojiacn.com
|
| 1 | hm.baidu.com |
laojiacn.com
|
| 1 | img.thethsdnadagvx.com |
laojiacn.com
|
| 1 | 365ty.8169idc.com |
laojiacn.com
|
| 42 | 8 |
This site contains links to these domains. Also see Links.
| Domain |
|---|
| 365ty.8600082999.com |
| Subject Issuer | Validity | Valid | |
|---|---|---|---|
| *.365ty.top YR1 |
2026-07-13 - 2026-10-11 |
3mo | crt.sh |
| *.8169idc.com YR1 |
2026-07-29 - 2026-10-27 |
3mo | crt.sh |
| img.thethsdnadagvx.com WE1 |
2026-08-11 - 2026-11-09 |
3mo | crt.sh |
| baidu.com GlobalSign RSA OV SSL CA 2018 |
2026-07-09 - 2027-01-24 |
7mo | crt.sh |
| *.aizhantj.com GlobalSign GCC R6 AlphaSSL CA 2025 |
2026-06-27 - 2027-01-12 |
7mo | crt.sh |
This page contains 1 frames:
Primary Page:
https://laojiacn.com/
Frame ID: 9EEDA43E93C610288A2D1CD6262027E9
Requests: 42 HTTP requests in this frame
Screenshot
Go Pro
Only in urlscan Pro
Use the Visual Search feature to find pages with visually similar screenshots.
Click for more information
Free trials of urlscan Pro are available.
Page Title
2026世界杯直播|足球直播|NBA直播|CCTV5在线直播-365体育Detected technologies
 Bootstrap
(UI frameworks)
Expand
Detected patterns
- <link[^>]* href=[^>]*?bootstrap(?:[^>]*?([0-9a-fA-F]{7,40}|[\d]+(?:.[\d]+(?:.[\d]+)?)?)|)[^>-]*?(?:\.min)?\.css
- (?:/|-)bootstrap(?:[^/]*?([0-9a-fA-F]{7,40}|[\d]+(?:\.[\d]+(?:\.[\d]+)?)?)|)[^/]*?(?:\.min)?\.js
 Font Awesome
(Font scripts)
Expand
Detected patterns
- (?:F|f)o(?:n|r)t-?(?:A|a)wesome(?:.*?([0-9a-fA-F]{7,40}|[\d]+(?:.[\d]+(?:.[\d]+)?)?)|)
 jQuery
(JavaScript libraries)
Expand
Detected patterns
- jquery
- /jquery(?:-(\d+\.\d+\.\d+))[/.-]
Page Statistics
1 Outgoing links
These are links going to different origins than the main page.
Search URL Search Domain Scan URL
Redirected requests
There were HTTP redirect chains for the following requests:
42 HTTP transactions
0 data transactions
| Method Protocol |
Status | Resource Path |
Size x-fer |
Time Latency |
Type MIME-Type |
IP Location |
|||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
|
GET H2 |
200 |
Primary Request
/
Show response
laojiacn.com/ |
84 KB 15 KB |
114ms
7ms |
Document
text/html |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
font-awesome.min.css
laojiacn.com/public/css/ |
21 KB 5 KB |
44ms
28ms |
Stylesheet
text/css |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
main.css
laojiacn.com/public/css/ |
39 KB 10 KB |
37ms
22ms |
Stylesheet
text/css |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
bootstrap.css
laojiacn.com/public/css/ |
124 KB 24 KB |
39ms
24ms |
Stylesheet
text/css |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
style.css
laojiacn.com/public/css/ |
54 KB 14 KB |
37ms
23ms |
Stylesheet
text/css |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
style.css
laojiacn.com/app/home/skins/default/ |
69 KB 15 KB |
39ms
25ms |
Stylesheet
text/css |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
jquery-3.2.1.min.js
Show response
laojiacn.com/public/js/ |
85 KB 33 KB |
30ms
25ms |
Script
application/javascript |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
bootstrap.min.js
Show response
laojiacn.com/public/js/ |
36 KB 11 KB |
31ms
27ms |
Script
application/javascript |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
hm.js
Show response
365ty.8169idc.com/js/ |
59 KB 14 KB |
735ms
349ms |
Script
application/javascript |
172.247.46.243 CNSERVERS LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
logo.png
laojiacn.com/uploadfile/logo/ |
460 KB 458 KB |
33ms
29ms |
Image
image/png |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
_raw3_size1200x80_dce44d54-7339-4d25-8236-e04699aeb3b1.gif
img.thethsdnadagvx.com/202601/ |
39 KB 39 KB |
68ms
24ms |
Image
image/gif |
172.67.194.33 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
titan_30324_0.jpg
img.365ty.top/article/ |
12 KB 12 KB |
87ms
10ms |
Image
image/jpeg |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
titan_29911_0.png
img.365ty.top/article/ |
11 KB 11 KB |
77ms
6ms |
Image
image/png |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
20221030152839_41199.png
img.365ty.top/article/ |
343 KB 340 KB |
81ms
10ms |
Image
image/png |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
zhibo.js
Show response
laojiacn.com/app/zhibo/js/ |
27 KB 11 KB |
11ms
5ms |
Script
application/javascript |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
titan_28913_0.png
img.365ty.top/article/ |
16 KB 16 KB |
77ms
8ms |
Image
image/png |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
titan_27830_0.png
img.365ty.top/article/ |
9 KB 9 KB |
80ms
11ms |
Image
image/png |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
titan_27781_0.png
img.365ty.top/article/ |
17 KB 18 KB |
76ms
7ms |
Image
image/png |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
titan_27493_0.png
img.365ty.top/article/ |
24 KB 24 KB |
20ms
18ms |
Image
image/png |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
titan_27301_0.png
img.365ty.top/article/ |
9 KB 9 KB |
25ms
24ms |
Image
image/png |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
titan_26636_0.png
img.365ty.top/article/ |
11 KB 11 KB |
23ms
19ms |
Image
image/png |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
titan_26522_0.png
img.365ty.top/article/ |
14 KB 14 KB |
21ms
20ms |
Image
image/png |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
titan_26277_0.jpg
img.365ty.top/article/ |
17 KB 17 KB |
19ms
19ms |
Image
image/jpeg |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
titan_26189_0.png
img.365ty.top/article/ |
25 KB 25 KB |
7ms
4ms |
Image
image/png |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
WX.jpg
laojiacn.com/public/images/ |
21 KB 9 KB |
10ms
7ms |
Image
image/jpeg |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
APP.jpg
laojiacn.com/public/images/ |
20 KB 10 KB |
10ms
7ms |
Image
image/jpeg |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
extend.func.js
Show response
laojiacn.com/app/home/js/ |
5 KB 2 KB |
13ms
8ms |
Script
application/javascript |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
common.js
Show response
laojiacn.com/public/js/ |
6 KB 2 KB |
11ms
6ms |
Script
application/javascript |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
hm.gif
hm.baidu.com/ |
43 B 636 B |
1231ms
541ms |
Image
image/gif |
14.215.182.140 No.31 |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
/
Show response
node92.aizhantj.com/tjjs/ |
35 KB 13 KB |
965ms
500ms |
Script
application/javascript |
43.169.32.101 ACE |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
push.js
Show response
zz.bdstatic.com/linksubmit/ |
308 B 562 B |
1527ms
614ms |
Script
application/x-javascript |
36.248.16.48 CHINA UNICOM Chin... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
ico_down.gif
laojiacn.com/public/images/ |
1 KB 1 KB |
28ms
23ms |
Image
image/gif |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
fontawesome-webfont.woff
laojiacn.com/public/font/ |
43 KB 43 KB |
13ms
12ms |
Font
font/woff |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
rcode.jpg
laojiacn.com/public/images/ |
8 KB 7 KB |
17ms
16ms |
Image
image/jpeg |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
/
Show response
node92.aizhantj.com/tjpv/ |
2 B 488 B |
341ms
340ms |
XHR
application/json |
43.169.32.101 ACE |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
s.gif
sp0.baidu.com/9_Q4simg2RQJ8t7jm9iCKT-xh_/ |
0 116 B |
519ms
281ms |
Image
text/plain |
98.98.225.192 Zenlayer Inc |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
zhibo
Show response
laojiacn.com/data/ |
46 B 341 B |
9ms
4ms |
XHR
text/html |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
favicon.ico
laojiacn.com/ |
70 KB 71 KB |
9ms
8ms |
Other
image/x-icon |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
zhibo
Show response
laojiacn.com/data/ |
46 B 341 B |
5ms
4ms |
XHR
text/html |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
zhibo
Show response
laojiacn.com/data/ |
46 B 341 B |
6ms
6ms |
XHR
text/html |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
zhibo
Show response
laojiacn.com/data/ |
46 B 341 B |
6ms
5ms |
XHR
text/html |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
zhibo
Show response
laojiacn.com/data/ |
46 B 341 B |
53ms
27ms |
XHR
text/html |
139.162.11.114 Akamai Connected ... |
|||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||





























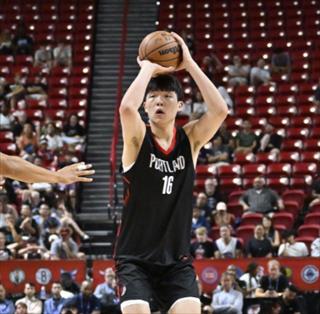








Verdicts & Comments Add Verdict or Comment
Potentially malicious activity detected
Disclaimer: These verdicts should be used to detect potentially malicious websites, not as a final verdict!
urlscan
Phishing against: Bet365 (Entertainment) Go ProOnly in urlscan Pro
25 JavaScript Window variables
These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.
function| $ function| jQuery boolean| _bdhm_loaded_5b787a01c0d19ee4f9c79ef1761250e1 object| _hmt object| mini_tangram_log_q1rich object| _mtj string| _0xodt number| _0xodt_ object| _0xa0c4 function| _0x3298 function| removeByValue object| Fn object| $that function| qh function| dj function| $$ function| toplist function| tsNotice function| selectSoccer_score function| selectnba function| selectScore function| selectshoot_goal function| selectnbas function| selectgoal boolean| _bdhm_loaded_huvb44fv7ai8 Cookies
Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.
| Domain/Path | Expires | Name / Value | |||
|---|---|---|---|---|---|
| .laojiacn.com/ | 1970-01-22 01:28:55 |
Name: Hm_lvt_5b787a01c0d19ee4f9c79ef1761250e1 Value: 1788199743 |
|||
| .laojiacn.com/ | 1969-12-31 23:59:59 |
Name: Hm_lpvt_5b787a01c0d19ee4f9c79ef1761250e1 Value: 1788199743 |
|||
| .laojiacn.com/ | 1969-12-31 23:59:59 |
Name: HMACCOUNT Value: C924673EB83EC08B |
|||
| .laojiacn.com/ | 1970-01-22 01:28:55 |
Name: Hm_tf_huvb44fv7ai Value: 1788199744 |
|||
| .laojiacn.com/ | 1970-01-22 01:28:55 |
Name: Hm_lvt_huvb44fv7ai Value: 1788199744 |
|||
| .laojiacn.com/ | 1969-12-31 23:59:59 |
Name: Hm_lpvt_huvb44fv7ai Value: 1788199744 |
|||
| .hm.baidu.com/ | 1970-01-22 02:19:19 |
Name: HMACCOUNT_BFESS Value: 82C88CAF7C008607 |
|||
| node92.aizhantj.com/ | 1970-01-21 17:03:29 |
Name: _aztj_sess Value: td1op0nlitgk6us86ng7c151d7 |
Security Headers
This page lists any security headers set by the main page. If you want to understand what these mean and how to use them, head on over to this page
| Header | Value |
|---|---|
| Strict-Transport-Security | max-age=31536000; includeSubDomains; preload |
Indicators
This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.
365ty.8169idc.com
hm.baidu.com
img.365ty.top
img.thethsdnadagvx.com
laojiacn.com
node92.aizhantj.com
sp0.baidu.com
zz.bdstatic.com
139.162.11.114
14.215.182.140
172.247.46.243
172.67.194.33
36.248.16.48
43.169.32.101
98.98.225.192
0f5dbaf15dd5e6c11c3543f52886700a41c1c153a53a18bf4333c7c1f240f596
0fc4e676b01f03c1a9371f66d7ccac76a679d0f882d142d53723f0aa56bddac4
1498533a53a2108cfa18d3456996c22bc2881d94f3218966010c341fd8bdf4db
18e6b5ff511b90edf098e62ac45ed9d6673a3eee10165d0de4164d4d02a3a77f
1bead6df36bd0e28f62d8df42022c440859bad1c407dfb3d620ab4540763a620
267129e712dbf0447655b18e0a49bc8dd934f939b78b564be0c1d4445df8dcaf
29359dc4ac743e37a0c4c64984bcfb2c8f3f5cb91cdefb8970e82cc2680de5da
30b2d43006c98bde7791fe401ad72a5f46ee980e4c8b1f720c5b70c2aab74963
36460e494e4c628443afded40b2743b5ede9a4a76fb4f7b9ef2345cc7e59fd64
3a8e26a459972dfa91a264eaa32c5b3de66f607fd2ba73060575305bc5298b5b
3c2327f43c65118cceb500c03ad9990c760d866fa6231f8ad79d68bab0c75025
43662f80a585327acf3baccb012dc0430620ff9160bef459a5d99d7acb7b0c21
44136fa355b3678a1146ad16f7e8649e94fb4fc21fe77e8310c060f61caaff8a
497aabc57e2e5428b57c3c75629123278e97359846c2ef667b55b52ec51db618
5d8a7f3dcd92b45499b673ea65ce4fd92e0c4f0a0314f3c200cef91c2fc24e57
5e413169859768e15c35940a6f2adc32be31eb2ebf8531e0cd60148e32ad4835
660334aecd515d852368e24f2d874a628154d33f601732baa3da30f7114a5a19
66b1579c7c30b74d34c2eb6f6c4ed1644666979e8e88b9ded346c9daa94e1bf1
7a9bc7cbebc13cc6dba29d40e7dbe900b04570835197d640191bae5adf3527d7
855285e30b58113c7f51819208b56cc855c4335ae24913e269578d6aa96c2595
856b021efed520d06c6238eb71746c8cdfcc0301d85a2cf78864cce5e2e36ce8
8e9186c0f1e0c69d882b6c7174d0d35922d7c0683feae7d3f37e7cacdff8c0ea
960997191d93dcfdd773e20ee17c1d1ab376c644672b798bc20e1b3b97f45acd
9b31cb28d98813191062105e1513cf54a50f9953bccb246cf3f001ae296190e7
9f27fe98e93a8421a06b47973bd78556044cb4657faa3f51abf64271fbd5dd77
a91757f82afebe860472fa8379a1bef2f8fa6a59a553084f92c1f655c5a84d0e
ab0f3c2befeb5edb94459b68ba8bb0158d022ee717f93db7b7ae0e42706b18f4
b7fbabd75917d65a7b44624fbc73e88a1a7bd3c4cad5485d03e82ccc7d18ea0d
bde39d1472ef777f9b9f9c8ddf5d19b541fa788aa92609c036172917b845ecfe
c16b4529c646e97bffeeb202b85a9be8b4ac10af1f4b7558825d92cdc6b8c755
c31f2003f1c93ac1e34b09f376d97a65da6e110bf451cf1e0e50a7946c5e7212
cf4724b2f736ed1a0ae6bc28f1ead963d9cd2c1fd87b6ef32e7799fc1c5c8bda
d3a518dea876de39f9e5dc1ffcdeb6c661aee25d8a62474386b664ef3bf1b40f
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
eaf33088c705f64753ce5793cbd59eec593162fe15548628cf31801a5a23409d
f04fc1fa0922eec1be6b63a83ecb5e28098aeaa3b6d8a09029ce67dc2aeb4c5d
f05741554c33063cf8d43de8fc418b1dc7f9fe37f41b9baf6c4047ff0c358059
fc825188c1e4afb01f0bb51f175918350aee80435545023e09e2be5febf9e2a9