
www.universe.com
151.101.66.87
Public Scan
Open in
urlscan Pro
https://www.universe.com/events/40-jahre-spezi-tickets-LWJ743 10yr old
Submission: On September 02 via api (September 2nd 2026, 1:09:11 am UTC) from IL — Scanned from US Go Pro
Only in urlscan Pro
- Select different country locations for Private Scans.
- Use a global network of additional scanning locations and residential IPs for scanning.
- Interact with pages while you are scanning them.
- Download files from remote websites.
- Scan websites on the Tor Network.
Summary
TLS certificate: Issued by GlobalSign Atlas R3 DV TLS CA 2025 Q3 on October 6th 2025. Valid for: 1yr.
This is the only time www.universe.com was scanned on urlscan.io!
urlscan.io Verdict: No classification
Domain & IP information
| IP Address | AS Autonomous System | ||
|---|---|---|---|
| 22 | 151.101.66.87 151.101.66.87 | 54113 (FASTLY) (FASTLY - Fastly) | |
| 1 | 172.217.114.4 172.217.114.4 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 151.101.66.217 151.101.66.217 | 54113 (FASTLY) (FASTLY - Fastly) | |
| 1 | 3.167.88.32 3.167.88.32 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 6 | 172.217.215.97 172.217.215.97 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 34.215.54.25 34.215.54.25 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 2 | 52.216.48.80 52.216.48.80 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 2 | 151.101.130.132 151.101.130.132 | 54113 (FASTLY) (FASTLY - Fastly) | |
| 1 | 172.217.118.4 172.217.118.4 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 3.167.88.49 3.167.88.49 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 2 | 44.220.127.32 44.220.127.32 | 14618 (AMAZON-AES) (AMAZON-AES - Amazon.com) | |
| 1 | 52.0.213.61 52.0.213.61 | 14618 (AMAZON-AES) (AMAZON-AES - Amazon.com) | |
| 1 | 142.250.9.138 142.250.9.138 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 142.250.9.154 142.250.9.154 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 45 | 15 |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-3-167-88-32.iad55.r.cloudfront.net
| cdn.amplitude.com 9yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: yo-in-f97.1e100.net
| www.googletagmanager.com 14yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: ec2-34-215-54-25.us-west-2.compute.amazonaws.com
| api.amplitude.com 10yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: s3-1.amazonaws.com
| s3.amazonaws.com 14yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-3-167-88-49.iad55.r.cloudfront.net
| t.contentsquare.net 9yr old |
ASN14618 (AMAZON-AES - Amazon.com, Inc., US)
PTR: ec2-44-220-127-32.compute-1.amazonaws.com
| c.contentsquare.net 9yr old |
ASN14618 (AMAZON-AES - Amazon.com, Inc., US)
PTR: ec2-52-0-213-61.compute-1.amazonaws.com
| k-aus1.contentsquare.net 6yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: yq-in-f138.1e100.net
| analytics.google.com 9yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: yq-in-f154.1e100.net
| stats.g.doubleclick.net 10yr old |
| Apex Domain Subdomains |
Transfer | |
|---|---|---|
| 24 |
universe.com
www.universe.com — Cisco Umbrella Rank: 239906 10yr old images.universe.com — Cisco Umbrella Rank: 452609 11yr old |
505 KB |
| 6 |
googletagmanager.com
www.googletagmanager.com — Cisco Umbrella Rank: 47 14yr old |
1 MB |
| 4 |
contentsquare.net
t.contentsquare.net — Cisco Umbrella Rank: 2757 9yr old c.contentsquare.net — Cisco Umbrella Rank: 4261 9yr old k-aus1.contentsquare.net — Cisco Umbrella Rank: 8952 6yr old |
128 KB |
| 2 |
amazonaws.com
s3.amazonaws.com 14yr old |
1 MB |
| 2 |
amplitude.com
cdn.amplitude.com — Cisco Umbrella Rank: 2232 9yr old api.amplitude.com — Cisco Umbrella Rank: 4438 10yr old |
26 KB |
| 2 |
googleapis.com
maps.googleapis.com — Cisco Umbrella Rank: 584 10yr old |
377 KB |
| 1 |
doubleclick.net
stats.g.doubleclick.net — Cisco Umbrella Rank: 157 10yr old |
550 B |
| 1 |
google.com
analytics.google.com — Cisco Umbrella Rank: 147 9yr old |
|
| 1 |
ravenjs.com
cdn.ravenjs.com — Cisco Umbrella Rank: 19801 13yr old |
14 KB |
| 0 |
cookielaw.org
Failed
cdn.cookielaw.org Failed 10yr old |
|
| 45 | 10 |
| Domain | Requested by | |
|---|---|---|
| 22 | www.universe.com |
www.universe.com
cdn.ravenjs.com |
| 6 | www.googletagmanager.com |
www.universe.com
www.googletagmanager.com |
| 2 | c.contentsquare.net |
www.universe.com
|
| 2 | images.universe.com |
www.universe.com
|
| 2 | s3.amazonaws.com |
www.universe.com
|
| 2 | maps.googleapis.com |
www.universe.com
cdn.ravenjs.com |
| 1 | stats.g.doubleclick.net |
www.googletagmanager.com
|
| 1 | analytics.google.com |
cdn.ravenjs.com
|
| 1 | k-aus1.contentsquare.net |
cdn.ravenjs.com
|
| 1 | t.contentsquare.net |
www.universe.com
|
| 1 | api.amplitude.com |
cdn.amplitude.com
|
| 1 | cdn.amplitude.com |
www.universe.com
|
| 1 | cdn.ravenjs.com |
www.universe.com
|
| 0 | cdn.cookielaw.org Failed |
www.googletagmanager.com
|
| 45 | 14 |
This site contains links to these domains. Also see Links.
| Domain |
|---|
| alumniimpressum.my.canva.site |
| maps.google.com |
| careers.universe.com |
| blog.universe.com |
| developers.universe.com |
| twitter.com |
| instagram.com |
| facebook.com |
| Subject Issuer | Validity | Valid | |
|---|---|---|---|
| *.comedystophelsinki.fi GlobalSign Atlas R3 DV TLS CA 2025 Q3 |
2025-10-06 - 2026-11-07 |
1yr | crt.sh |
| upload.video.google.com WE2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| cdn.ravenjs.com GlobalSign Atlas R3 DV TLS CA 2025 Q4 |
2025-11-10 - 2026-12-12 |
1yr | crt.sh |
| cdn.amplitude.com Amazon RSA 2048 M01 |
2025-10-15 - 2026-11-13 |
1yr | crt.sh |
| *.google-analytics.com WE2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| *.amplitude.com Amazon RSA 2048 M04 |
2025-12-02 - 2026-12-30 |
1yr | crt.sh |
| s3.amazonaws.com Amazon RSA 2048 M04 |
2025-11-18 - 2026-11-06 |
1yr | crt.sh |
| images.universe.com Certainly Intermediate R1 |
2026-08-31 - 2026-09-30 |
1mo | crt.sh |
| t.contentsquare.net Amazon RSA 2048 M04 |
2025-12-09 - 2027-01-07 |
1yr | crt.sh |
| dep.bf.contentsquare.net YR2 |
2026-08-24 - 2026-11-22 |
3mo | crt.sh |
| dep-malka.bf.contentsquare.net YR1 |
2026-08-24 - 2026-11-22 |
3mo | crt.sh |
| *.google.com WE2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| *.g.doubleclick.net WE2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
This page contains 1 frames:
Primary Page:
https://www.universe.com/events/40-jahre-spezi-tickets-LWJ743
Frame ID: 68780096A9BB1E61ACFA0C3CCCAE5E9E
Requests: 46 HTTP requests in this frame
Screenshot
Go Pro
Only in urlscan Pro
Use the Visual Search feature to find pages with visually similar screenshots.
Click for more information
Free trials of urlscan Pro are available.
Page Title
40 Jahre SPEZI - UniverseDetected technologies
 Google Maps
(Maps)
Expand
Detected patterns
- //maps\.google(?:apis)?\.com/maps/api/js
 React
(JavaScript frameworks)
Expand
Detected patterns
- <[^>]+data-react
 Amazon S3
(CDN)
Expand
Detected patterns
- s3[^ ]*\.amazonaws\.com/
 Amplitude
(Analytics)
Expand
Detected patterns
- cdn\.(?:segment.+)?amplitude(?:\.com|-plugins)
 Contentsquare
(Analytics)
Expand
Detected patterns
- \.contentsquare\.net/
 DoubleClick Floodlight
(Advertising)
Expand
Detected patterns
- \.doubleclick\.net
 Google Analytics
(Analytics)
Expand
Detected patterns
- googletagmanager\.com/gtag/js
 Google Tag Manager
(Tag managers)
Expand
Detected patterns
- googletagmanager\.com/gtm\.js
- \.googletagmanager\.com/
Page Statistics
8 Outgoing links
Go Pro
Only in urlscan Pro
Effortlessly use any on-page link as a pivot to discover other pages pointing to the exact same destination. Seamlessly trace both specific URLs and broader domains to uncover hidden connection networks and map out backlink relationships with ease.
Click for more information
Free trials of urlscan Pro are available.
These are links going to different origins than the main page.
Title: https://alumnispezi.my.canva.site/impressum
Search URL Search Domain Scan URL
Title: Get Directions
Search URL Search Domain Scan URL
Title: Jobs
Search URL Search Domain Scan URL
Title: Blog
Search URL Search Domain Scan URL
Title: Developers
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Redirected requests
There were HTTP redirect chains for the following requests:
45 HTTP transactions
Go Pro
Only in urlscan Pro
Inspect WebSocket connections, examine POST data effortlessly, and track overlap counts in real time. Features live search and filtering across all HTTP output, complete with full response metadata for deep analysis.
Click for more information
Free trials of urlscan Pro are available.
1 data transactions
| Method Protocol |
Status | Resource Path |
Size x-fer |
Time Latency |
Type MIME-Type |
IP Location |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
|
GET H2 |
200 |
Primary Request
40-jahre-spezi-tickets-LWJ743
Show response
www.universe.com/events/ |
2 KB 2 KB |
15046ms
1451ms |
Document
text/html |
151.101.66.87 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
main.e83be6906324d5d74acd.css
www.universe.com/fan/ |
3 KB 1 KB |
343ms
314ms |
Stylesheet
text/css |
151.101.66.87 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
47.e83be6906324d5d74acd.js
Show response
www.universe.com/fan/ |
390 KB 111 KB |
343ms
315ms |
Script
text/javascript |
151.101.66.87 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
main.e83be6906324d5d74acd.js
Show response
www.universe.com/fan/ |
29 KB 9 KB |
2133ms
2105ms |
Script
text/javascript |
151.101.66.87 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
29.e83be6906324d5d74acd.js
Show response
www.universe.com/fan/ |
18 KB 2 KB |
429ms
423ms |
Script
text/javascript |
151.101.66.87 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
30.e83be6906324d5d74acd.js
Show response
www.universe.com/fan/ |
13 KB 5 KB |
445ms
437ms |
Script
text/javascript |
151.101.66.87 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
0.e83be6906324d5d74acd.js
Show response
www.universe.com/fan/ |
19 KB 7 KB |
1737ms
1733ms |
Script
text/javascript |
151.101.66.87 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
1.e83be6906324d5d74acd.css
www.universe.com/fan/ |
5 KB 1 KB |
1792ms
1788ms |
Stylesheet
text/css |
151.101.66.87 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
1.e83be6906324d5d74acd.js
Show response
www.universe.com/fan/ |
13 KB 4 KB |
1760ms
1757ms |
Script
text/javascript |
151.101.66.87 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
2.e83be6906324d5d74acd.css
www.universe.com/fan/ |
1 KB 866 B |
1774ms
1771ms |
Stylesheet
text/css |
151.101.66.87 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
2.e83be6906324d5d74acd.js
Show response
www.universe.com/fan/ |
43 KB 15 KB |
1288ms
1287ms |
Script
text/javascript |
151.101.66.87 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
3.e83be6906324d5d74acd.js
Show response
www.universe.com/fan/ |
20 KB 6 KB |
1266ms
1257ms |
Script
text/javascript |
151.101.66.87 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
35.e83be6906324d5d74acd.css
www.universe.com/fan/ |
51 KB 11 KB |
1511ms
1509ms |
Stylesheet
text/css |
151.101.66.87 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
35.e83be6906324d5d74acd.js
Show response
www.universe.com/fan/ |
375 KB 113 KB |
1294ms
1286ms |
Script
text/javascript |
151.101.66.87 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
js
Show response
maps.googleapis.com/maps/api/ |
1 MB 376 KB |
1265ms
510ms |
Script
text/javascript |
172.217.114.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
raven.min.js
Show response
cdn.ravenjs.com/3.26.4/ |
37 KB 14 KB |
3736ms
2867ms |
Script
application/javascript |
151.101.66.217 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
amplitude-4.4.0-min.gz.js
Show response
cdn.amplitude.com/libs/ |
74 KB 25 KB |
3268ms
1888ms |
Script
application/javascript |
3.167.88.32 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
gtm.js
Show response
www.googletagmanager.com/ |
717 KB 243 KB |
3284ms
2156ms |
Script
application/javascript |
172.217.215.97 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
gtm.js
Show response
www.googletagmanager.com/ |
397 KB 132 KB |
2017ms
890ms |
Script
application/javascript |
172.217.215.97 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
graphql
Show response
www.universe.com/ |
4 KB 2 KB |
1074ms
1073ms |
Fetch
application/json |
151.101.66.87 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
graphql
Show response
www.universe.com/ |
186 B 932 B |
625ms
623ms |
Fetch
application/json |
151.101.66.87 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET DATA |
200 OK |
truncated
/ |
44 B 0 |
Image
image/webp |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Graphik-Regular-Web.woff2
www.universe.com/fonts/Graphik/ |
30 KB 30 KB |
1230ms
1224ms |
Font
application/font-woff2 |
151.101.66.87 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Graphik-Medium-Web.woff2
www.universe.com/fonts/Graphik/ |
33 KB 33 KB |
1507ms
1501ms |
Font
application/font-woff2 |
151.101.66.87 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
/
Show response
api.amplitude.com/ |
7 B 137 B |
3446ms
1544ms |
XHR
text/html |
34.215.54.25 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
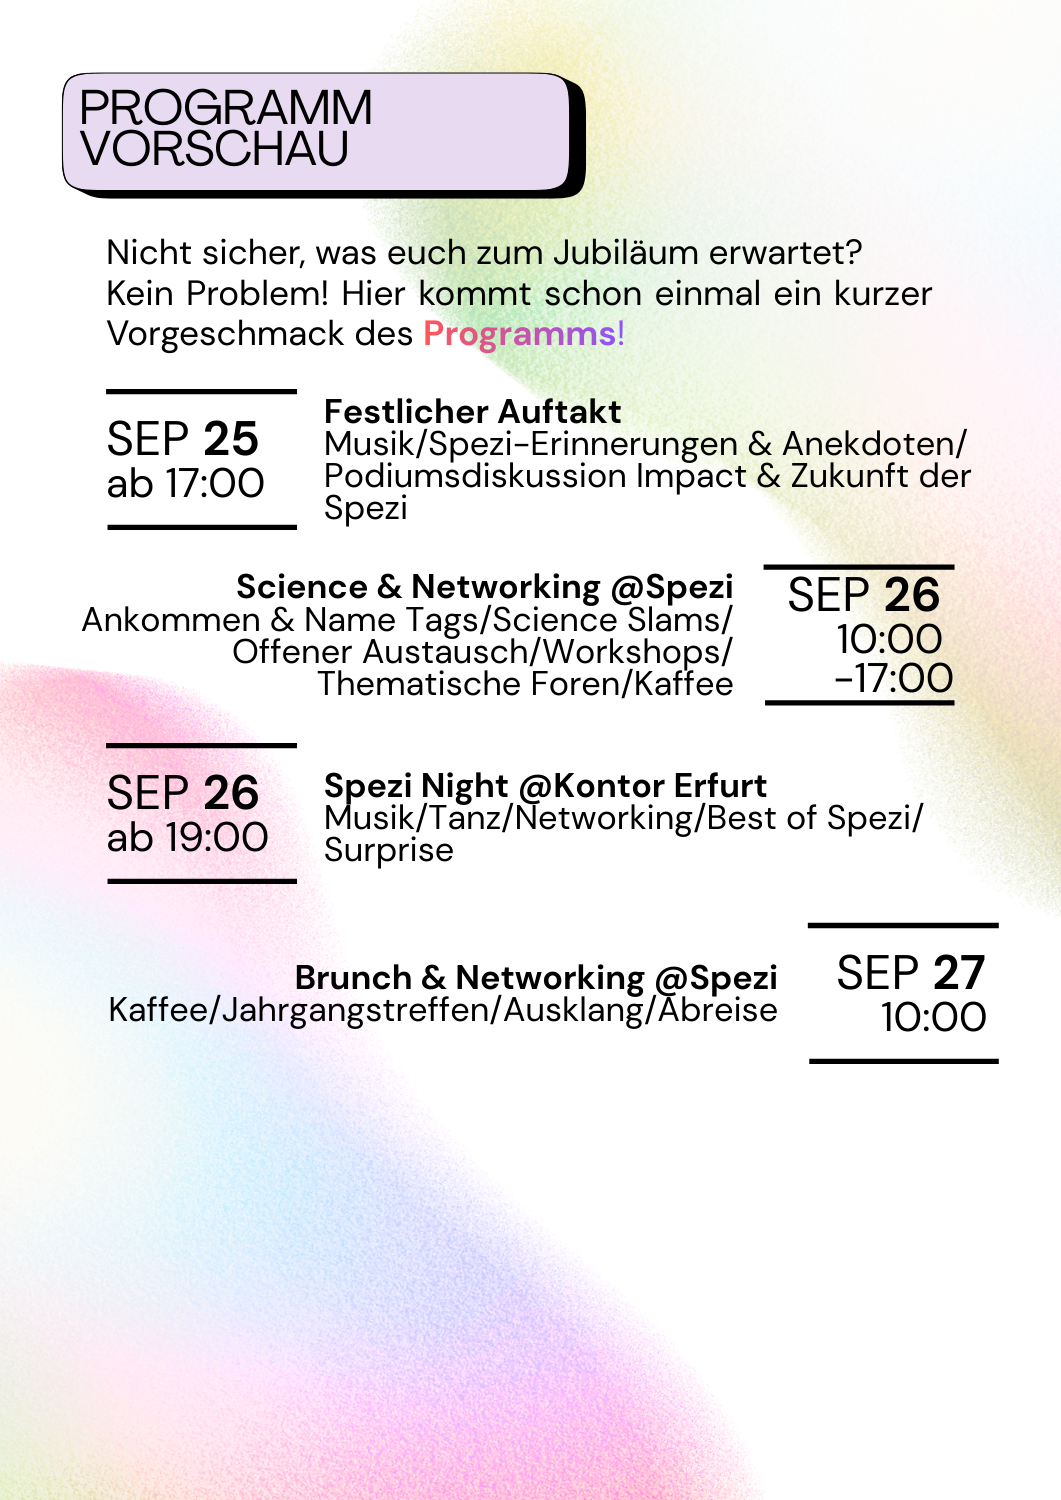
25984544cce38f3c22ac8604b72537bb-Programm3.png
s3.amazonaws.com/uniiverse_production/attachments/ |
1 MB 1 MB |
1566ms
548ms |
Image
image/png |
52.216.48.80 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
40Jahre.png
s3.amazonaws.com/uniiverse_production/photos/69b54eb1b39b010034297571/thumb/ |
4 KB 4 KB |
1597ms
534ms |
Image
image/png |
52.216.48.80 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
/
images.universe.com/1a62e348-32e3-406c-88ac-26d3deeaa675/-/progressive/yes/-/scale_crop/2220x888/center/-/blur/500/-/quality/lighter/-/format/webp/ |
11 KB 11 KB |
1291ms
477ms |
Image
image/webp |
151.101.130.132 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
/
images.universe.com/1a62e348-32e3-406c-88ac-26d3deeaa675/-/progressive/yes/-/scale_crop/2220x888/center/-/quality/lighter/-/format/webp/ |
78 KB 78 KB |
1227ms
412ms |
Image
image/webp |
151.101.130.132 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
lineto-circular-pro-medium.woff2
www.universe.com/fonts/Circular-Pro-subsetted/ |
33 KB 33 KB |
1007ms
1006ms |
Font
application/font-woff2 |
151.101.66.87 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
embed2.js
Show response
www.universe.com/ |
73 KB 25 KB |
923ms
922ms |
Script
text/javascript |
151.101.66.87 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
graphql
Show response
www.universe.com/ |
419 B 719 B |
522ms
516ms |
Fetch
application/json |
151.101.66.87 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
gen_204
Show response
maps.googleapis.com/maps/api/mapsjs/ |
3 B 330 B |
937ms
935ms |
XHR
application/json |
172.217.118.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
otSDKStub.js
cdn.cookielaw.org/scripttemplates/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
gtm.js
Show response
www.googletagmanager.com/ |
636 KB 191 KB |
1106ms
1104ms |
Script
application/javascript |
172.217.215.97 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
gtm.js
Show response
www.googletagmanager.com/ |
655 KB 188 KB |
1054ms
1053ms |
Script
application/javascript |
172.217.215.97 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
gtm.js
Show response
www.googletagmanager.com/ |
716 KB 193 KB |
1937ms
1936ms |
Script
application/javascript |
172.217.215.97 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
uxa.js
Show response
t.contentsquare.net/ss/48432/14/ |
432 KB 127 KB |
830ms
398ms |
Script
application/javascript |
3.167.88.49 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
js
Show response
www.googletagmanager.com/gtag/ |
522 KB 174 KB |
531ms
531ms |
Script
application/javascript |
172.217.215.97 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
54fb10e9-0a52-4041-8454-af493a197fe2
https://www.universe.com/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
204 |
pageview
c.contentsquare.net/ |
0 264 B |
758ms
303ms |
Image
text/plain |
44.220.127.32 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
204 |
dvar
c.contentsquare.net/ |
0 19 B |
731ms
302ms |
Image
text/plain |
44.220.127.32 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
recording
Show response
k-aus1.contentsquare.net/v2/ |
0 183 B |
941ms
444ms |
XHR
text/plain |
52.0.213.61 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
collect
analytics.google.com/g/ |
0 0 |
792ms
352ms |
Fetch
text/plain |
142.250.9.138 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
collect
stats.g.doubleclick.net/g/ |
0 550 B |
827ms
295ms |
Ping
text/plain |
142.250.9.154 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
favicon.ico
www.universe.com/ |
34 KB 3 KB |
996ms
995ms |
Other
image/vnd.microsoft.icon |
151.101.66.87 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||




Failed requests
These URLs were requested, but there was no response received. You will also see them in the list above.
- Domain
- cdn.cookielaw.org
- URL
- https://cdn.cookielaw.org/scripttemplates/otSDKStub.js
- Domain
- www.universe.com
- URL
- blob:https://www.universe.com/54fb10e9-0a52-4041-8454-af493a197fe2
Verdicts & Comments Add Verdict or Comment
71 JavaScript Window variables
Go Pro
Only in urlscan Pro
Inspect and pivot on JavaScript variables, identifiers, and other key site metadata data with urlscan Pro. Reveal and search on client-side frameworks, runtime variables, and custom values.
Click for more information
Free trials of urlscan Pro are available.
These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.
object| 0 object| 1 object| 2 object| SSR_DATA object| webpackJsonp function| setImmediate function| clearImmediate object| digitalData object| amplitude object| dataLayer object| __core-js_shared__ object| core function| _ boolean| SUPPORTS_WEBP string| CSRF_TOKEN object| Raven object| google_tag_manager object| google_tag_data function| emitEcommerceEvent function| OptanonWrapper object| google object| module$exports$google3$maps$api$javascript$geometry$lat_lng_bounds object| module$exports$google3$maps$api$javascript$marker$marker object| litHtmlVersions object| litElementVersions object| reactiveElementVersions function| postscribe object| google_tag_manager_external object| OptanonLN function| setCookieFunc object| ceddl object| gtmCCV object| $u object| _uxa object| CS_CONF function| csSetTimeout function| csSetInterval function| csQueueMicrotask function| csClearTimeout function| csClearInterval function| csFileReader function| csSymbol object| CSPureWindow function| csDate object| csJSON function| csArray function| csString function| csURL function| csMutationObserver object| csScreen function| csRegExp object| csquerySelector object| csquerySelectorAll function| csIntersectionObserver function| csNodechildNodes function| csNodeparentNode function| csNodenextSibling function| csNodefirstChild function| csNodenodeType function| csElementshadowRoot function| csElementmatches function| csElementwebkitMatchesSelector function| csHTMLImageElementsrc function| csEventtarget function| csNavigatorsendBeacon object| CSPathComputation object| CSCurrentScript object| CSQ_TAGS object| UXAnalytics object| CSFrameCommunication object| gaGlobal8 Cookies
Go Pro
Only in urlscan Pro
Review, search, and pivot on browser cookies and persistence site data to see how a site tracks users and keeps sessions alive across visits.
Click for more information
Free trials of urlscan Pro are available.
Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.
| Domain/Path | Expires | Name / Value | |||
|---|---|---|---|---|---|
| .universe.com/ | 1970-01-22 02:21:11 |
Name: amplitude_id_8f3073b2e3efb3028708aeca4bff06f5universe.com Value: eyJkZXZpY2VJZCI6ImZiNGVkOTIyLWRiN2YtNDE5ZC05ZGQ1LWM1MDgzYzAzNjU2ZFIiLCJ1c2VySWQiOm51bGwsIm9wdE91dCI6ZmFsc2UsInNlc3Npb25JZCI6MTc4ODMxMTM3Njc1OSwibGFzdEV2ZW50VGltZSI6MTc4ODMxMTM3Njc2MSwiZXZlbnRJZCI6MSwiaWRlbnRpZnlJZCI6MCwic2VxdWVuY2VOdW1iZXIiOjF9 |
|||
| .universe.com/ | 1970-01-21 17:28:23 |
Name: _session_id_v2 Value: 4f5825ae6af749bcefb47de7b6f72ebf |
|||
| .universe.com/ | 1970-01-22 02:14:35 |
Name: _cs_c Value: 0 |
|||
| .universe.com/ | 1969-12-31 23:59:59 |
Name: _cs_cvars Value: %7B%221%22%3A%5B%22Page%20Name%22%2C%22UNI_DE%3A%20Event%20Display%20Page%22%5D%2C%222%22%3A%5B%22Page%20Type%22%2C%22Event%20Display%20Page%22%5D%2C%223%22%3A%5B%22Page%20Channel%22%2C%22event-display-page%22%5D%2C%224%22%3A%5B%22Platform%22%2C%22fan%22%5D%2C%225%22%3A%5B%22eventID%22%2C%2269b549413475a7003c27482f%22%5D%2C%226%22%3A%5B%22eventName%22%2C%2240%20Jahre%20SPEZI%22%5D%2C%227%22%3A%5B%22eventDate%22%2C%229%2F25%2F2026%22%5D%2C%228%22%3A%5B%22eventTime%22%2C%225%3A00%3A00%20PM%22%5D%2C%229%22%3A%5B%22universeHostID%22%2C%2269b3c8d4d8369b00241c4477%22%5D%2C%2210%22%3A%5B%22universeHostName%22%2C%22Alumni%20des%20Spezialschulteils%20des%20Albert-Schweitzer%20Gymnasiums%20Erfurt%20e.V.%22%5D%2C%2211%22%3A%5B%22primaryCategory%22%2C%22Other%22%5D%2C%2212%22%3A%5B%22virtualEvent%22%2C%220%22%5D%2C%2213%22%3A%5B%22referringURL%22%2C%22null%22%5D%2C%2214%22%3A%5B%22venueName%22%2C%22Vilniuser%20Str.%2017a%22%5D%2C%2215%22%3A%5B%22destinationURL%22%2C%22https%3A%2F%2Fwww.universe.com%2Fevents%2F40-jahre-spezi-tickets-LWJ743%22%5D%7D |
|||
| .universe.com/ | 1970-01-22 02:14:35 |
Name: _cs_id Value: 8a597349-11b8-a3b3-eb5c-0ee1e48d76f7.1788311385.1.1788311385.1788311385.1.1822475385307.1.x |
|||
| .universe.com/ | 1970-01-21 16:45:13 |
Name: _cs_s Value: 1.5.U.9.1788313185324 |
|||
| .universe.com/ | 1970-01-22 02:21:11 |
Name: _ga_KV7N0RNNVS Value: GS2.1.s1788311386$o1$g0$t1788311386$j60$l0$h0 |
|||
| .universe.com/ | 1970-01-22 02:21:11 |
Name: _ga Value: GA1.1.1496400389.1788311386 |
4 Console Messages
A page may trigger messages to the console to be logged. These are often error messages about being unable to load a resource or execute a piece of JavaScript. Sometimes they also provide insight into the technology behind a website.
| Source | Level | URL Text |
|---|
Security Headers
This page lists any security headers set by the main page. If you want to understand what these mean and how to use them, head on over to this page
| Header | Value |
|---|---|
| Content-Security-Policy | frame-ancestors 'none' |
| Strict-Transport-Security | max-age=300 |
Indicators
This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.
analytics.google.com
api.amplitude.com
c.contentsquare.net
cdn.amplitude.com
cdn.cookielaw.org
cdn.ravenjs.com
images.universe.com
k-aus1.contentsquare.net
maps.googleapis.com
s3.amazonaws.com
stats.g.doubleclick.net
t.contentsquare.net
www.googletagmanager.com
www.universe.com
cdn.cookielaw.org
www.universe.com
142.250.9.138
142.250.9.154
151.101.130.132
151.101.66.217
151.101.66.87
172.217.114.4
172.217.118.4
172.217.215.97
3.167.88.32
3.167.88.49
34.215.54.25
44.220.127.32
52.0.213.61
52.216.48.80
18fd3da54fd37e2fee6e3082f22ce2e5a620658bf6c652aa1a404933ccf6abd3
1979cdb3a04a31bc01ac8d03a1ab2a5319af49cba6f588438ce4b915cff9e257
19e69dd83299f0d990474aaf142c8571e5a5b7b1bac49f9abc3bb8af5ab0de4e
1b79f5c97e038ca5f0bd9f576d8eea6b8d1384f99c60bed365ca27203f37a2ac
1b88af4c7e73fd993fdaf250987cb0736580c6775476f5f5d6186fe48ea4f195
21afbb14fed7d57a101b6731c8d2ce255b509dc59576136a4263cbd169998f08
384004188c62fdd4db6f8efa3d61a7f07de31cf40c4a4e68b782ebbe45c59034
3b6205206b5c515bb685b81ad82ecedf1264a0f1b6b0a99b2d89ce18fe30bc5e
457d055bb53515a0f840a45bc86f92279cedee41854079bebeeb4a11ac445a02
474e0ca5faefb2a997b3f3f3f302e2511ae8aa6a08724f8721ddc5509550ef0e
47832521343485b4d15fca2a9a549a3844e1302422989761c116067a1721491b
599ec78a1e02e60f4647edc298d70d5dc334bb952b17721fc86a584eb20b253d
5b55ecdce83144119c5bd6995bcd262d84e9bd61996689ce66d20a24b8e1db23
5d43ad1efcbeb5df1140ead9562576e674f84059ccef9ed5070dadb6c1aca014
5e221d0b42b74fb818977d9d0efc6068ad81cbbcf8ab574a592dc5dc51120fcf
7a2fabda53f27194f9bda012ba941435547584b7c2b8a411f12c178fa48efc49
9673c5eddbe5d0cb1b31b23073ec86baba902ebc6dacccf70fc693e08319ca8b
9673d3638087ae43cf9b1ad74e8c4d2b3c90229fa756a66efe73f859005a8db0
997eca07cd5e82e88501b1d3535bf3e12b2ce40f94840ae6ed0266a6037e0947
aa4d27e0d0c0172667e24d953344b058b7f16c6ef7dcc54a8910878f1d050cae
aee408847d35e44e99430f0979c3357b85fe8dbb4535a494301198adbee85f27
b699cbc01e16c3c4cdb1c9a4b466b8225018b48c7aeeab33ea8390181872428b
bd25bde9fc4427cd6f3babcb8f888fe6174ca48881c103e243d4c6f83f30aab6
be326433e8a389a8ed9a952d8de7396c5b8ac0560a64239d31875e628ec7ed17
beb91144ec587749f998dd94356f11a265b6669d590aba2df32b78e14710cc68
c320f1fbd915775b9ffb4921129d8d9f6cfae03d8d4556b3a6f499a5d7ea599a
c46efba5b3c31461bd0816d99497c8613392e775daed1150165bd21b92282bb9
c5e717cb6ccb90f8dbe52d5c1b1f0635fe3912a06f549b2787dc5d5e6e01de1c
c69f2d79ecc613dfaf0bc5ede0d137826589b012246f8194e795fa8402a66788
ca3d163bab055381827226140568f3bef7eaac187cebd76878e0b63e9e442356
cb4649fd872c4eb3e0cd2411c5f97e0105ecc040d27f16bad0daae45d212ed4d
d4e39183ffda8f1d6aad85a92fc7d966fe03eedf822539ffa42e3c75b2d824e2
d655d569e9bfd547214eeeaff92d024c2d173a81298cf5abaeea7ec53ebd49da
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
e611c5ac5ab6344065ee64754fb2200fa17ab514a98d145287ff05a4b67834e5
edb5566621043c33e295e376238126e8070a1391a618cb8a9cab24e3d7b8959c
f048861a16eb05af71c637408e23b2e8fd13c1a263bc9c523a69650c70adceb5
f221106ad702504a418b35227a656ee9b0045b2ff49f362082e8b4fc28b148a5
f5999fb06294842c1af92d1165e4fab075687bb04ba90467840afbc550650545
f78a239d7604dd25ef827ac0936720efe0b4da0b0ad7b2c71430009b533a3808