
www.thomastonsavingsbank.com
192.140.7.143
Public Scan
Open in
urlscan Pro
https://thombank.net/ 4yr old
Effective URL:
https://www.thomastonsavingsbank.com/ 14yr old
Submission: On September 03 via automatic, source certstream-suspicious (September 3rd 2026, 3:36:05 pm UTC) — Scanned from DE Go Pro
Only in urlscan Pro
- Select different country locations for Private Scans.
- Use a global network of additional scanning locations and residential IPs for scanning.
- Interact with pages while you are scanning them.
- Download files from remote websites.
- Scan websites on the Tor Network.
Summary
TLS certificate: Issued by Go Daddy Secure Certificate Authority... on December 17th 2025. Valid for: 1yr.
This is the only time www.thomastonsavingsbank.com was scanned on urlscan.io!
urlscan.io Verdict: No classification
Domain & IP information
| IP Address | AS Autonomous System | ||
|---|---|---|---|
| 1 1 | 188.114.96.3 188.114.96.3 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 54 | 192.140.7.143 192.140.7.143 | 54420 (COCC-ISP1) (COCC-ISP1 - COCC) | |
| 1 | 142.251.14.97 142.251.14.97 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 2 | 151.101.193.91 151.101.193.91 | 54113 (FASTLY) (FASTLY - Fastly) | |
| 1 | 18.67.13.98 18.67.13.98 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 2 | 18.173.187.89 18.173.187.89 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 3 | 18.227.200.194 18.227.200.194 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 5 | 34.203.115.134 34.203.115.134 | 14618 (AMAZON-AES) (AMAZON-AES - Amazon.com) | |
| 4 | 99.84.152.44 99.84.152.44 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 6 | 18.173.205.74 18.173.205.74 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 1 | 142.251.127.95 142.251.127.95 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 184.24.77.167 184.24.77.167 | 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.) | |
| 1 | 184.24.77.135 184.24.77.135 | 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.) | |
| 3 | 142.251.14.94 142.251.14.94 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 3 | 18.173.187.29 18.173.187.29 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 6 | 142.251.156.4 142.251.156.4 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 2 | 142.251.153.4 142.251.153.4 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 2 | 142.251.110.155 142.251.110.155 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 142.251.127.149 142.251.127.149 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 4 | 142.251.151.119 142.251.151.119 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 192.178.183.119 192.178.183.119 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 2 | 172.217.117.4 172.217.117.4 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 3 | 172.64.150.82 172.64.150.82 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 2 | 104.18.37.174 104.18.37.174 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 52.7.4.58 52.7.4.58 | 14618 (AMAZON-AES) (AMAZON-AES - Amazon.com) | |
| 1 1 | 34.7.37.3 34.7.37.3 | 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC) | |
| 1 | 35.204.89.238 35.204.89.238 | 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC) | |
| 111 | 26 |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| thombank.net 4yr old |
ASN54420 (COCC-ISP1 - COCC, US)
| www.thomastonsavingsbank.com 14yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: pm-in-f97.1e100.net
| www.googletagmanager.com 14yr old |
ASN54113 (FASTLY - Fastly, Inc., US)
| fe.sitedataprocessing.com 11yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-18-67-13-98.muc50.r.cloudfront.net
| gt-pixel-prod.groundtruth.com 1yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-18-173-187-89.muc50.r.cloudfront.net
| api.glia.com 6yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: ec2-18-227-200-194.us-east-2.compute.amazonaws.com
| px.premion.com 1yr old |
ASN14618 (AMAZON-AES - Amazon.com, Inc., US)
PTR: ec2-34-203-115-134.compute-1.amazonaws.com
| arttrk.com 8yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-99-84-152-44.fra56.r.cloudfront.net
| cdn.segmint.net 9yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-18-173-205-74.fra56.r.cloudfront.net
| libs.salemove.com 7yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: lcfrai-in-f95.1e100.net
| fonts.googleapis.com 10yr old |
ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL)
PTR: a184-24-77-167.deploy.static.akamaitechnologies.com
| use.typekit.net 14yr old |
ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL)
PTR: a184-24-77-135.deploy.static.akamaitechnologies.com
| p.typekit.net 14yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: pm-in-f94.1e100.net
| fonts.gstatic.com 10yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-18-173-187-29.muc50.r.cloudfront.net
| api.salemove.com 9yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: bz-in-f155.1e100.net
| googleads.g.doubleclick.net 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: lcfrai-in-f149.1e100.net
| static.doubleclick.net 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
| www.google.com 14yr old | |
| www.youtube.com 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: lcfraw-in-f119.1e100.net
| i.ytimg.com 10yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| connect.segmint.net 9yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| connect.segmint.net 9yr old | |
| maprtb.segmint.net 6yr old |
ASN14618 (AMAZON-AES - Amazon.com, Inc., US)
PTR: ec2-52-7-4-58.compute-1.amazonaws.com
| client-logger.salemove.com 8yr old |
ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US)
PTR: 3.37.7.34.bc.googleusercontent.com
| um.simpli.fi 10yr old |
ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US)
PTR: 238.89.204.35.bc.googleusercontent.com
| tag.simpli.fi 10yr old |
| Apex Domain Subdomains |
Transfer | |
|---|---|---|
| 54 |
thomastonsavingsbank.com
www.thomastonsavingsbank.com 14yr old |
4 MB |
| 11 |
youtube.com
www.youtube.com — Cisco Umbrella Rank: 105 10yr old |
997 KB |
| 10 |
salemove.com
libs.salemove.com — Cisco Umbrella Rank: 22428 7yr old api.salemove.com — Cisco Umbrella Rank: 21672 9yr old client-logger.salemove.com — Cisco Umbrella Rank: 19112 8yr old |
418 KB |
| 9 |
segmint.net
cdn.segmint.net — Cisco Umbrella Rank: 55710 9yr old connect.segmint.net — Cisco Umbrella Rank: 63101 9yr old maprtb.segmint.net — Cisco Umbrella Rank: 159816 6yr old |
43 KB |
| 5 |
arttrk.com
arttrk.com — Cisco Umbrella Rank: 6123 8yr old |
655 B |
| 3 |
doubleclick.net
1 redirects
googleads.g.doubleclick.net — Cisco Umbrella Rank: 68 10yr old static.doubleclick.net — Cisco Umbrella Rank: 287 10yr old |
665 B |
| 3 |
gstatic.com
fonts.gstatic.com — Cisco Umbrella Rank: 31 10yr old |
110 KB |
| 3 |
googleapis.com
fonts.googleapis.com — Cisco Umbrella Rank: 46 10yr old jnn-pa.googleapis.com — Cisco Umbrella Rank: 344 5yr old |
3 KB |
| 3 |
premion.com
px.premion.com — Cisco Umbrella Rank: 34174 1yr old |
1 KB |
| 2 |
simpli.fi
1 redirects
um.simpli.fi — Cisco Umbrella Rank: 1180 10yr old tag.simpli.fi — Cisco Umbrella Rank: 5932 10yr old |
1 KB |
| 2 |
typekit.net
use.typekit.net — Cisco Umbrella Rank: 544 14yr old p.typekit.net — Cisco Umbrella Rank: 660 14yr old |
1019 B |
| 2 |
glia.com
api.glia.com — Cisco Umbrella Rank: 17325 6yr old |
14 KB |
| 2 |
sitedataprocessing.com
fe.sitedataprocessing.com — Cisco Umbrella Rank: 42737 11yr old |
6 KB |
| 1 |
ytimg.com
i.ytimg.com — Cisco Umbrella Rank: 124 10yr old |
31 KB |
| 1 |
google.com
www.google.com — Cisco Umbrella Rank: 3 14yr old |
24 KB |
| 1 |
groundtruth.com
gt-pixel-prod.groundtruth.com — Cisco Umbrella Rank: 345211 1yr old |
20 KB |
| 1 |
googletagmanager.com
www.googletagmanager.com — Cisco Umbrella Rank: 49 14yr old |
145 KB |
| 1 |
thombank.net
1 redirects
thombank.net 4yr old |
592 B |
| 111 | 18 |
| Domain | Requested by | |
|---|---|---|
| 54 | www.thomastonsavingsbank.com |
www.thomastonsavingsbank.com
|
| 11 | www.youtube.com |
www.thomastonsavingsbank.com
www.googletagmanager.com www.youtube.com |
| 6 | libs.salemove.com |
api.glia.com
libs.salemove.com |
| 5 | arttrk.com |
www.thomastonsavingsbank.com
|
| 4 | connect.segmint.net |
cdn.segmint.net
|
| 4 | cdn.segmint.net |
www.thomastonsavingsbank.com
cdn.segmint.net |
| 3 | api.salemove.com |
libs.salemove.com
|
| 3 | fonts.gstatic.com |
fonts.googleapis.com
www.youtube.com |
| 3 | px.premion.com |
www.googletagmanager.com
px.premion.com |
| 2 | jnn-pa.googleapis.com |
www.youtube.com
|
| 2 | googleads.g.doubleclick.net |
1 redirects
www.youtube.com
|
| 2 | api.glia.com |
www.googletagmanager.com
api.glia.com |
| 2 | fe.sitedataprocessing.com |
www.thomastonsavingsbank.com
fe.sitedataprocessing.com |
| 1 | pubsub.salemove.com | |
| 1 | tag.simpli.fi |
connect.segmint.net
|
| 1 | maprtb.segmint.net |
connect.segmint.net
|
| 1 | um.simpli.fi | 1 redirects |
| 1 | client-logger.salemove.com |
libs.salemove.com
|
| 1 | i.ytimg.com |
www.youtube.com
|
| 1 | www.google.com |
www.youtube.com
|
| 1 | static.doubleclick.net |
www.youtube.com
|
| 1 | p.typekit.net |
use.typekit.net
|
| 1 | use.typekit.net |
www.thomastonsavingsbank.com
|
| 1 | fonts.googleapis.com |
www.thomastonsavingsbank.com
|
| 1 | gt-pixel-prod.groundtruth.com |
www.thomastonsavingsbank.com
|
| 1 | www.googletagmanager.com |
www.thomastonsavingsbank.com
|
| 1 | thombank.net | 1 redirects |
| 111 | 27 |
This site contains links to these domains. Also see Links.
| Subject Issuer | Validity | Valid | |
|---|---|---|---|
| www.thomastonsavingsbank.com Go Daddy Secure Certificate Authority - G2 |
2025-12-17 - 2026-12-19 |
1yr | crt.sh |
| *.google-analytics.com WE2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| data.processwebsitedata.com Certainly Intermediate R1 |
2026-08-16 - 2026-09-15 |
1mo | crt.sh |
| *.groundtruth.com Amazon RSA 2048 M01 |
2025-11-14 - 2026-12-12 |
1yr | crt.sh |
| *.glia.com Amazon RSA 2048 M01 |
2026-08-17 - 2027-03-02 |
7mo | crt.sh |
| *.premion.com Amazon RSA 2048 M01 |
2026-04-27 - 2026-11-10 |
7mo | crt.sh |
| adxcel-ec2.com Amazon RSA 2048 M01 |
2026-06-20 - 2027-01-03 |
7mo | crt.sh |
| *.segmint.net Amazon RSA 2048 M01 |
2026-08-03 - 2027-02-16 |
7mo | crt.sh |
| upload.video.google.com WE2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| use.typekit.net DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2026-05-29 - 2026-12-13 |
7mo | crt.sh |
| *.gstatic.com WE2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| *.google.com WE2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| *.doubleclick.net WE2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| edgestatic.com WR2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| segmint.net WE1 |
2026-08-31 - 2026-11-29 |
3mo | crt.sh |
| *.simpli.fi DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2025-10-23 - 2026-11-23 |
1yr | crt.sh |
This page contains 3 frames:
Primary Page:
https://www.thomastonsavingsbank.com/
Frame ID: 54E6DF1BCED14B15377AA708FF0C2E68
Requests: 94 HTTP requests in this frame
Frame:
https://www.youtube.com/embed/14dMooRPHSQ?rel=0&showinfo=0&enablejsapi=1&controls=1
Frame ID: 5C222C9AF1653FD15AA7D902EA64363D
Requests: 15 HTTP requests in this frame
Frame:
https://connect.segmint.net/iframe/doughnut/en1xxXxz6j
Frame ID: FC0E72104CC8C2508DEAF67A0CEC8B83
Requests: 3 HTTP requests in this frame
Screenshot
Go Pro
Only in urlscan Pro
Use the Visual Search feature to find pages with visually similar screenshots.
Click for more information
Free trials of urlscan Pro are available.
Page Title
Thomaston Savings Bank | CT Personal & Business BankingPage URL History
Go Pro
Only in urlscan Pro
Search our real-time database of newly observed domains and
hostnames. Pivot on different attributes, and setup keyword alerts for
newly observed domains.
Click for more information
Free trials of urlscan Pro are available.
Show full URLs
-
https://thombank.net/
HTTP 301
https://www.thomastonsavingsbank.com/ Page URL
Detected technologies
 Concrete CMS
(CMS)
Expand
Detected patterns
- /concrete/js/
 Bootstrap
(UI frameworks)
Expand
Detected patterns
- (?:/|-)bootstrap(?:[^/]*?([0-9a-fA-F]{7,40}|[\d]+(?:\.[\d]+(?:\.[\d]+)?)?)|)[^/]*?(?:\.min)?\.js
 YouTube
(Video players)
Expand
Detected patterns
- \.youtube\.com/
 Vue.js
(JavaScript frameworks)
Expand
Detected patterns
- (?:/([\d.]+))?/vue(?:\.min)?\.js
 Cloudflare Bot Management
(Security)
Expand
Detected patterns
 DoubleClick Floodlight
(Advertising)
Expand
Detected patterns
- \.doubleclick\.net
 Glia
(Live chat)
Expand
Detected patterns
- api\.glia\.com/
 Google Tag Manager
(Tag managers)
Expand
Detected patterns
- <!-- (?:End )?Google Tag Manager -->
- googletagmanager\.com/gtm\.js
- \.googletagmanager\.com/
 Premion
(Advertising)
Expand
Detected patterns
- px\.premion\.com/
 Simpli.fi
(Advertising)
Expand
Detected patterns
- \.simpli\.fi
Page Statistics
12 Outgoing links
These are links going to different origins than the main page.
Title: GET
Search URL Search Domain Scan URL
Title: Pay My Loan
Search URL Search Domain Scan URL
Title: Log In
Search URL Search Domain Scan URL
Title: iFi University
Search URL Search Domain Scan URL
Title: Forgot Password
Search URL Search Domain Scan URL
Title: Apply Now
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Title: WORX
Search URL Search Domain Scan URL
Page URL History
This captures the URL locations of the websites, including HTTP redirects and client-side redirects via JavaScript or Meta fields.
-
https://thombank.net/
HTTP 301
https://www.thomastonsavingsbank.com/ Page URL
Redirected requests
There were HTTP redirect chains for the following requests:
Request Chain 93- https://googleads.g.doubleclick.net/pagead/id HTTP 302
- https://googleads.g.doubleclick.net/pagead/id?slf_rd=1
- https://um.simpli.fi/segmint HTTP 302
- https://maprtb.segmint.net/rtb/simpli-fi/cookie-mapper?simpli-fi-id=52AC7AF5E8BB4A4FBCD9AF30B3057C9F
111 HTTP transactions
6 data transactions
| Method Protocol |
Status | Resource Path |
Size x-fer |
Time Latency |
Type MIME-Type |
IP Location |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
|
GET H/1.1 |
200 OK |
Primary Request
/
Show response
www.thomastonsavingsbank.com/ Redirect Chain
|
285 KB 78 KB |
588ms
245ms |
Document
text/html |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
combined.min.css
www.thomastonsavingsbank.com/packages/worx/themes/worx/css/ |
450 KB 62 KB |
491ms
199ms |
Stylesheet
text/css |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
THOM_150th_main-website-logo.svg
www.thomastonsavingsbank.com/packages/worx/themes/worx/images/ |
21 KB 8 KB |
556ms
105ms |
Image
image/svg+xml |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
tsb-lock-active.svg
www.thomastonsavingsbank.com/packages/worx/themes/worx/images/ |
7 KB 3 KB |
150ms
150ms |
Image
image/svg+xml |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
tsb-lock-inactive.svg
www.thomastonsavingsbank.com/packages/worx/themes/worx/images/ |
2 KB 2 KB |
99ms
98ms |
Image
image/svg+xml |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
tsb-mobile-menu.svg
www.thomastonsavingsbank.com/packages/worx/themes/worx/images/ |
724 B 842 B |
98ms
97ms |
Image
image/svg+xml |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
tsb-mobile-menu-close.svg
www.thomastonsavingsbank.com/packages/worx/themes/worx/images/ |
423 B 812 B |
98ms
98ms |
Image
image/svg+xml |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
tsb-search-icon.svg
www.thomastonsavingsbank.com/packages/worx/themes/worx/images/ |
4 KB 2 KB |
538ms
214ms |
Image
image/svg+xml |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
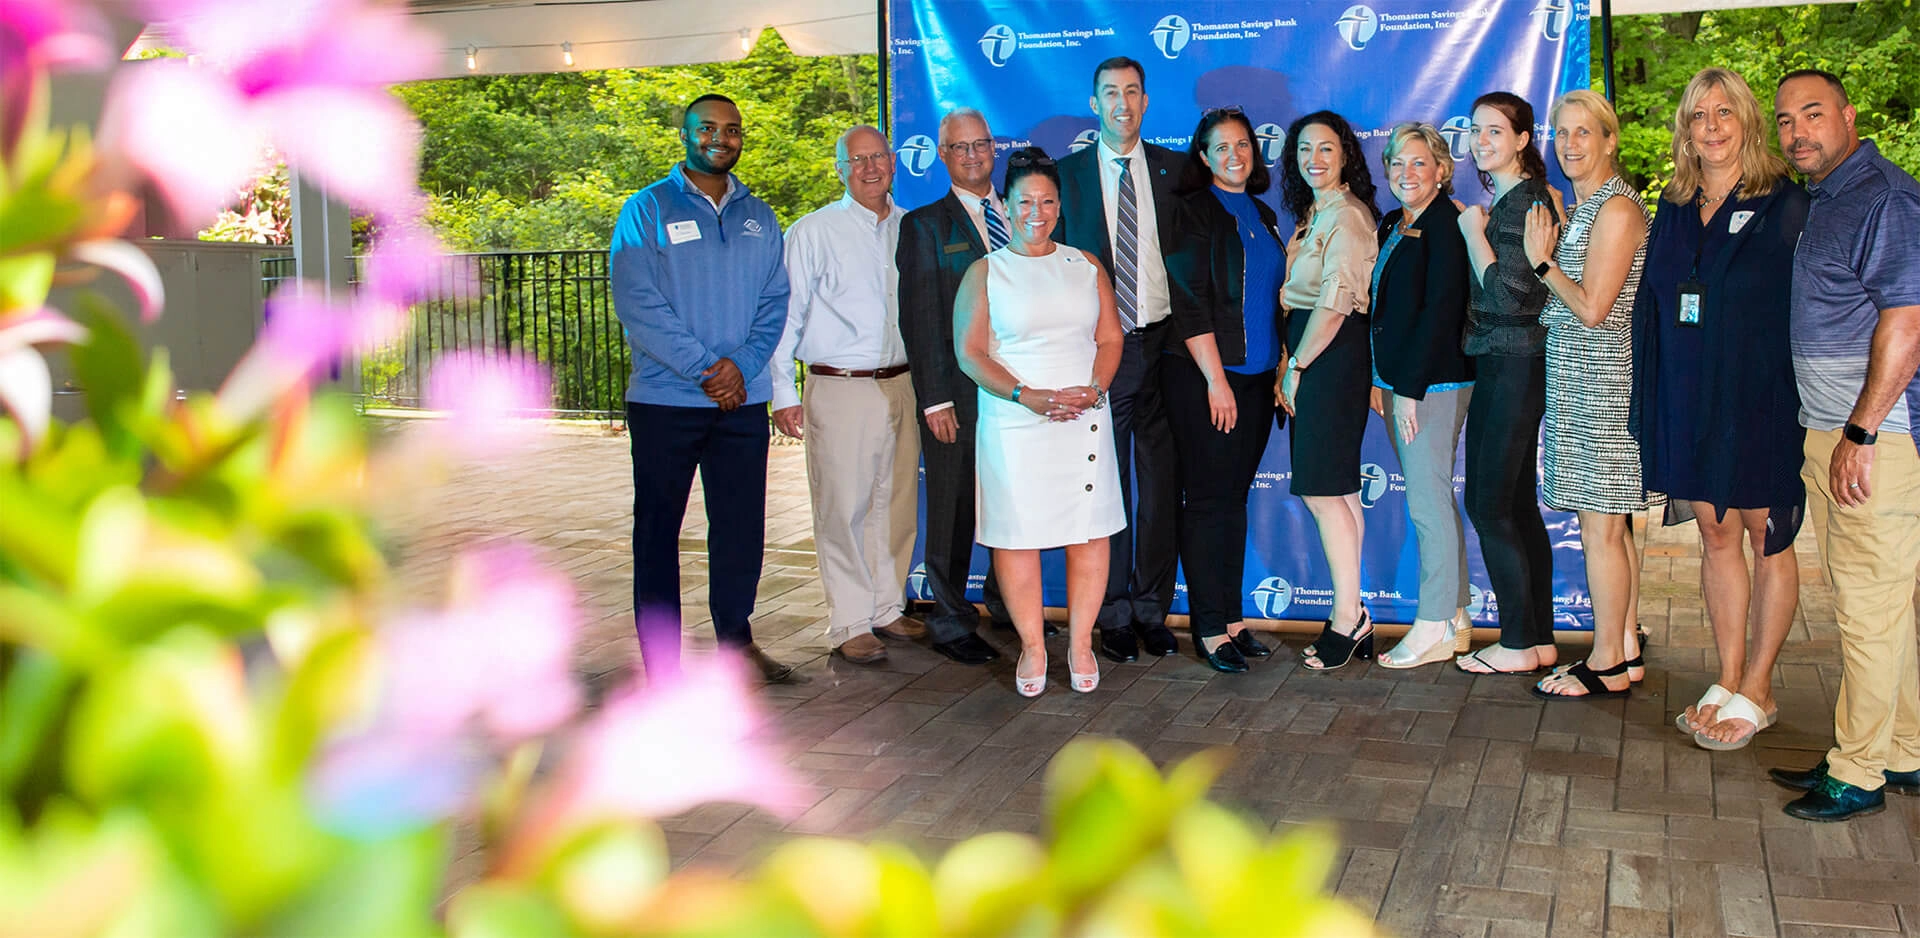
custom_1920x1080_proportionalTSB-foundation-night-thumbnail_R2-v1-id1134-2x.webp
www.thomastonsavingsbank.com/webp/ |
529 KB 530 KB |
100ms
99ms |
Image
image/webp |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
frontend.css
www.thomastonsavingsbank.com/concrete/css/features/imagery/ |
9 KB 3 KB |
486ms
195ms |
Stylesheet
text/css |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
frontend.css
www.thomastonsavingsbank.com/concrete/css/features/social/ |
480 B 712 B |
480ms
188ms |
Stylesheet
text/css |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
tsb-app-icon.svg
www.thomastonsavingsbank.com/packages/worx/themes/worx/images/ |
4 KB 2 KB |
449ms
104ms |
Image
image/svg+xml |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
fdic-digital-sign-white.svg
www.thomastonsavingsbank.com/packages/worx/themes/worx/images/ |
14 KB 4 KB |
585ms
104ms |
Image
image/svg+xml |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
tsb-horizontal-logo.svg
www.thomastonsavingsbank.com/packages/worx/themes/worx/images/ |
19 KB 8 KB |
474ms
189ms |
Image
image/svg+xml |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
gtm.js
Show response
www.googletagmanager.com/ |
450 KB 145 KB |
66ms
38ms |
Script
application/javascript |
142.251.14.97 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
zLND0IyCxk-611c074b.js
Show response
fe.sitedataprocessing.com/cscripts/ |
19 KB 6 KB |
156ms
120ms |
Script
application/javascript |
151.101.193.91 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
pixel.v1.js
Show response
gt-pixel-prod.groundtruth.com/ |
51 KB 20 KB |
90ms
38ms |
Script
application/javascript |
18.67.13.98 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
salemove_integration.js
Show response
api.glia.com/ |
6 KB 6 KB |
73ms
29ms |
Script
application/javascript |
18.173.187.89 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
pixel.js
Show response
px.premion.com/ |
883 B 1 KB |
436ms
205ms |
Script
application/javascript |
18.227.200.194 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
/
arttrk.com/pixel/ |
43 B 131 B |
395ms
101ms |
Image
image/gif |
34.203.115.134 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
/
arttrk.com/pixel/ |
43 B 131 B |
393ms
99ms |
Image
image/gif |
34.203.115.134 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
/
arttrk.com/pixel/ |
43 B 131 B |
425ms
108ms |
Image
image/gif |
34.203.115.134 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
/
arttrk.com/pixel/ |
43 B 131 B |
426ms
109ms |
Image
image/gif |
34.203.115.134 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
/
arttrk.com/pixel/ |
43 B 131 B |
427ms
106ms |
Image
image/gif |
34.203.115.134 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
visitor_config
Show response
api.glia.com/ |
12 KB 8 KB |
260ms
259ms |
XHR
application/json |
18.173.187.89 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
ProcessStats.aspx
Show response
fe.sitedataprocessing.com/fewv1/ |
241 B 489 B |
161ms
160ms |
Script
text/javascript |
151.101.193.91 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
segmint.min.js
Show response
cdn.segmint.net/ |
16 KB 16 KB |
57ms
14ms |
Script
application/javascript |
99.84.152.44 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
07e214898ec6b75629748251e8528608.png
www.thomastonsavingsbank.com/application/files/cache/thumbnails/ |
303 KB 304 KB |
98ms
98ms |
Image
image/png |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
bf7cd8341c020a359488b1d406a2c260.png
www.thomastonsavingsbank.com/application/files/cache/thumbnails/ |
298 KB 299 KB |
110ms
110ms |
Image
image/png |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
866f688c5f0271b22767c7903cfae8d6.png
www.thomastonsavingsbank.com/application/files/cache/thumbnails/ |
306 KB 306 KB |
99ms
99ms |
Image
image/png |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
e7b2f8fff4abc2aaa0436a1be5616eae.png
www.thomastonsavingsbank.com/application/files/cache/thumbnails/ |
175 KB 176 KB |
101ms
101ms |
Image
image/png |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
5ffacaa64642b3ab91857580cef1f8fd.png
www.thomastonsavingsbank.com/application/files/cache/thumbnails/ |
348 KB 348 KB |
99ms
98ms |
Image
image/png |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
16d726cf6deba293d9dfefee1628b696.png
www.thomastonsavingsbank.com/application/files/cache/thumbnails/ |
154 KB 154 KB |
101ms
101ms |
Image
image/png |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
fdic-digital-sign.svg
www.thomastonsavingsbank.com/packages/worx/themes/worx/images/ |
13 KB 4 KB |
103ms
103ms |
Image
image/svg+xml |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
iFi.png
www.thomastonsavingsbank.com/packages/worx/themes/worx/images/ |
262 KB 262 KB |
99ms
99ms |
Image
image/png |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
Mutuals%20Matter%20logo.png
www.thomastonsavingsbank.com/packages/worx/themes/worx/images/ |
59 KB 59 KB |
103ms
101ms |
Image
image/png |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
ab-seal-horizontal-large-US.jpg
www.thomastonsavingsbank.com/packages/worx/themes/worx/images/ |
114 KB 115 KB |
111ms
111ms |
Image
image/jpeg |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
Equal_Housing_FDIC.svg
www.thomastonsavingsbank.com/packages/worx/themes/worx/images/ |
8 KB 3 KB |
105ms
104ms |
Image
image/svg+xml |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
klaro
Show response
www.thomastonsavingsbank.com/api/js/ |
2 KB 1 KB |
278ms
278ms |
Script
application/javascript |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
bootstrap.js
Show response
www.thomastonsavingsbank.com/concrete/js/ |
79 KB 23 KB |
103ms
102ms |
Script
application/javascript |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
vue.js
Show response
www.thomastonsavingsbank.com/concrete/js/ |
105 KB 38 KB |
105ms
104ms |
Script
application/javascript |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
klaro-no-css.js
Show response
www.thomastonsavingsbank.com/packages/worx/assets/js/plugins/ |
175 KB 53 KB |
108ms
108ms |
Script
application/javascript |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
utm-helper.js
Show response
www.thomastonsavingsbank.com/packages/worx/assets/js/ |
1 KB 1 KB |
98ms
98ms |
Script
application/javascript |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
main.js
Show response
www.thomastonsavingsbank.com/packages/worx/assets/js/ |
34 KB 11 KB |
105ms
105ms |
Script
application/javascript |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
view.js
Show response
www.thomastonsavingsbank.com/packages/worx/blocks/hero/js/ |
431 B 819 B |
98ms
98ms |
Script
application/javascript |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
view.js
Show response
www.thomastonsavingsbank.com/packages/worx/blocks/callout/js/ |
2 KB 1 KB |
98ms
97ms |
Script
application/javascript |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
frontend.js
Show response
www.thomastonsavingsbank.com/concrete/js/features/imagery/ |
25 KB 9 KB |
101ms
101ms |
Script
application/javascript |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
view.js
Show response
www.thomastonsavingsbank.com/packages/worx/blocks/icons/js/ |
2 KB 1 KB |
105ms
105ms |
Script
application/javascript |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
bootstrapper-6d8d81066.js
Show response
libs.salemove.com/visitor/ |
623 KB 164 KB |
54ms
16ms |
Script
text/javascript |
18.173.205.74 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
webcomponents_es5-6d8d81066.js
Show response
libs.salemove.com/visitor/ |
936 B 1 KB |
8ms
8ms |
Script
text/javascript |
18.173.205.74 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
log-pixel
Show response
px.premion.com/ |
31 B 207 B |
204ms
203ms |
XHR
application/javascript |
18.227.200.194 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
OPTIONS H2 |
204 |
log-pixel
px.premion.com/ Frame |
0 0 |
475ms
257ms |
Preflight
|
18.227.200.194 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
css2
fonts.googleapis.com/ |
40 KB 3 KB |
58ms
31ms |
Stylesheet
text/css |
142.251.127.95 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
hms8anu.css
use.typekit.net/ |
1 KB 847 B |
228ms
190ms |
Stylesheet
text/css |
184.24.77.167 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
p.css
p.typekit.net/ |
5 B 172 B |
96ms
52ms |
Stylesheet
text/css |
184.24.77.135 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
o-0bIpQlx3QUlC5A4PNB6Ryti20_6n1iPHjc5a7duw.woff2
fonts.gstatic.com/s/notosans/v42/ |
35 KB 35 KB |
30ms
13ms |
Font
font/woff2 |
142.251.14.94 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
ga6daw1J5X9T9RW6j9bNVls-hfgvz8JcMofYTYf6D30.woff2
fonts.gstatic.com/s/notoserif/v33/ |
36 KB 36 KB |
25ms
8ms |
Font
font/woff2 |
142.251.14.94 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
custom_636x636_exactTSB-Home-Hero1-v1-id1026.webp
www.thomastonsavingsbank.com/webp/ |
99 KB 99 KB |
453ms
101ms |
Image
image/webp |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
custom_636x636_exactTSB-Home-Hero2-v1-id1025.webp
www.thomastonsavingsbank.com/webp/ |
85 KB 86 KB |
440ms
111ms |
Image
image/webp |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
custom_636x636_exactTSB-Home-Hero3-v1-id1024.webp
www.thomastonsavingsbank.com/webp/ |
108 KB 108 KB |
594ms
103ms |
Image
image/webp |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
OPTIONS H/1.1 |
200 OK |
3e427405-3eab-4969-829d-78b54d8d939d.json
cdn.segmint.net/ Frame |
0 0 |
310ms
291ms |
Preflight
|
99.84.152.44 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
3e427405-3eab-4969-829d-78b54d8d939d.json
Show response
cdn.segmint.net/ |
312 B 959 B |
316ms
315ms |
XHR
application/json |
99.84.152.44 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
tsb-left-arrow-white.svg
www.thomastonsavingsbank.com/packages/worx/themes/worx/images/ |
1 KB 1 KB |
99ms
98ms |
Image
image/svg+xml |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET DATA |
200 OK |
truncated
/ |
380 B 0 |
Image
image/svg+xml |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
TSB-Wedges.svg
www.thomastonsavingsbank.com/packages/worx/themes/worx/images/ |
2 KB 1 KB |
98ms
98ms |
Image
image/svg+xml |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
custom_1920x1080_proportionalTSB-foundation-night-thumbnail_R2-v1-id1134.webp
www.thomastonsavingsbank.com/webp/ |
529 KB 530 KB |
99ms
98ms |
Image
image/webp |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
custom_575x352_exacttsb-personal-checking-young-woman-on-phone-v2-id227.webp
www.thomastonsavingsbank.com/webp/ |
60 KB 61 KB |
637ms
97ms |
Image
image/webp |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
custom_575x352_exacttsb-personal-loans-man-on-laptop-v2-id228.webp
www.thomastonsavingsbank.com/webp/ |
40 KB 40 KB |
659ms
120ms |
Image
image/webp |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
custom_575x352_exacttsb-business-express-loan-woman-drinking-beverage-v2-id229.webp
www.thomastonsavingsbank.com/webp/ |
56 KB 56 KB |
749ms
101ms |
Image
image/webp |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
206 Partial Content |
24-THOM-391_Goal-Getter-Tool-Walkthrough-With-Music_FINAL-CUT_R1-V1.mp4
www.thomastonsavingsbank.com/application/files/8217/1941/2435/ |
3 MB 0 |
112ms
111ms |
Media
video/mp4 |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET DATA |
200 OK |
truncated
/ |
547 B 0 |
Image
image/svg+xml |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET DATA |
200 OK |
truncated
/ |
552 B 0 |
Image
image/svg+xml |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET DATA |
200 OK |
truncated
/ |
177 B 0 |
Image
image/svg+xml |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET DATA |
200 OK |
truncated
/ |
515 B 0 |
Image
image/svg+xml |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET DATA |
200 OK |
truncated
/ |
242 B 0 |
Image
image/svg+xml |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
tsb-location.svg
www.thomastonsavingsbank.com/packages/worx/themes/worx/images/ |
1 KB 1 KB |
98ms
98ms |
Image
image/svg+xml |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
check.png
www.thomastonsavingsbank.com/packages/worx/themes/worx/images/ |
3 KB 4 KB |
109ms
109ms |
Image
image/png |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
fa-solid-900.woff2
www.thomastonsavingsbank.com/packages/worx/themes/worx/css/webfonts/ |
76 KB 77 KB |
146ms
100ms |
Font
font/woff2 |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
fa-brands-400.woff2
www.thomastonsavingsbank.com/packages/worx/themes/worx/css/webfonts/ |
75 KB 76 KB |
352ms
101ms |
Font
font/woff2 |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
visitor-app.3d4beb9b.min.js
Show response
libs.salemove.com/ |
666 KB 196 KB |
13ms
12ms |
Script
text/javascript |
18.173.205.74 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
visitor-app.3d4beb9b.default.css
libs.salemove.com/ |
266 KB 39 KB |
11ms
10ms |
Stylesheet
text/css |
18.173.205.74 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
b93f9a4661e794
Show response
api.salemove.com/visitor_app/3d4beb9b/sites/6c238ca4-39d0-43d4-b03c-6bc1658ee055/custom_locales/en-us-chat/ |
15 KB 5 KB |
96ms
35ms |
XHR
application/json |
18.173.187.29 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
gva-custom-chat-renderer.869c56b.js
Show response
libs.salemove.com/ |
29 KB 10 KB |
19ms
19ms |
Script
text/javascript |
18.173.205.74 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
gva-custom-chat-renderer.869c56b.css
libs.salemove.com/ |
13 KB 3 KB |
11ms
11ms |
Stylesheet
text/css |
18.173.205.74 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H/1.1 |
200 OK |
alert-status
Show response
www.thomastonsavingsbank.com/json/ |
2 KB 2 KB |
874ms
253ms |
Fetch
application/json |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
6132
Show response
www.thomastonsavingsbank.com/get_latest_article/ |
2 KB 3 KB |
1063ms
433ms |
Fetch
application/json |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
14dMooRPHSQ
Show response
www.youtube.com/embed/ Frame 5C22 |
151 KB 63 KB |
171ms
125ms |
Document
text/html |
142.251.156.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
iframe_api
Show response
www.youtube.com/ |
993 B 3 KB |
76ms
38ms |
Script
text/javascript |
142.251.153.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
www-widgetapi.js
Show response
www.youtube.com/s/player/9470c977/www-widgetapi.vflset/ |
26 KB 9 KB |
8ms
7ms |
Script
text/javascript |
142.251.153.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
www-player.css
www.youtube.com/s/player/9470c977/ Frame 5C22 |
530 KB 57 KB |
10ms
9ms |
Stylesheet
text/css |
142.251.156.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
m=root,base
www.youtube.com/s/_/ytembeds/_/ss/k=ytembeds.base.jlNy0Xafd2w.L.W.O/am=AAAAQA/d=1/br=1/rs=AGKMywEQTXRn9SDhfarMeY5rFdSNXgxtEw/ Frame 5C22 |
0 409 B |
14ms
14ms |
Stylesheet
text/css |
142.251.156.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
KFO7CnqEu92Fr1ME7kSn66aGLdTylUAMa3yUBA.woff2
fonts.gstatic.com/s/roboto/v48/ Frame 5C22 |
39 KB 39 KB |
24ms
9ms |
Font
font/woff2 |
142.251.14.94 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
m=root,base
Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.XNkxQbJvN0Y.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywHVWumEt-3jpGegUoWIf6nrHsXpWQ/ Frame 5C22 |
456 KB 155 KB |
13ms
11ms |
Script
text/javascript |
142.251.156.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
base.js
Show response
www.youtube.com/s/player/9470c977/player_embed_es6.vflset/de_DE/ Frame 5C22 |
2 MB 472 KB |
18ms
17ms |
Script
text/javascript |
142.251.156.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
id
Show response
googleads.g.doubleclick.net/pagead/ Frame 5C22 Redirect Chain
|
100 B 146 B |
29ms
28ms |
XHR
application/json |
142.251.110.155 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
ad_status.js
Show response
static.doubleclick.net/instream/ Frame 5C22 |
29 B 496 B |
68ms
15ms |
Script
text/javascript |
142.251.127.149 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
m=r78Drb
Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.XNkxQbJvN0Y.2021.O/ck=ytembeds.base.jlNy0Xafd2w.L.W.O/am=AAAAQA/d=1/exm=base,root/excm=base,root/ed=1/br=1/rs=AGKMywHhmN1MQPeRwxyTmK-bg5YLnGy... Frame 5C22 |
907 KB 219 KB |
7ms
7ms |
Script
text/javascript |
142.251.156.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
Nnzuu5J_F_O4BdIqIrU2lZhdT-H-buEFYIxLjbvxu_0.js
Show response
www.google.com/js/th/ Frame 5C22 |
62 KB 24 KB |
29ms
13ms |
Script
text/javascript |
142.251.151.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
m=cwx9N
Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.XNkxQbJvN0Y.2021.O/ck=ytembeds.base.jlNy0Xafd2w.L.W.O/am=AAAAQA/d=1/exm=base,r78Drb,root/excm=base,root/ed=1/br=1/rs=AGKMywHhmN1MQPeRwxyTmK-b... Frame 5C22 |
65 KB 17 KB |
8ms
8ms |
Script
text/javascript |
142.251.151.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
sddefault.webp
i.ytimg.com/vi_webp/14dMooRPHSQ/ Frame 5C22 |
30 KB 31 KB |
92ms
57ms |
Image
image/webp |
192.178.183.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
OPTIONS H2 |
200 |
sources_triggered
api.salemove.com/overseer/ Frame |
0 0 |
113ms
113ms |
Preflight
text/plain |
18.173.187.29 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
201 |
sources_triggered
Show response
api.salemove.com/overseer/ |
2 B 455 B |
131ms
129ms |
XHR
application/json |
18.173.187.29 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
204 |
generate_204
www.youtube.com/ Frame 5C22 |
0 10 B |
7ms
7ms |
Image
text/plain |
142.251.151.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
OPTIONS H2 |
200 |
GenerateIT
jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/ Frame |
0 0 |
96ms
60ms |
Preflight
text/html |
172.217.117.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
GenerateIT
Show response
jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/ Frame 5C22 |
94 B 304 B |
26ms
24ms |
XHR
application/json+protobuf |
172.217.117.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
custom_416x416_exactAugust_Promos_Thumbnail-v1-id1142.webp
www.thomastonsavingsbank.com/webp/ |
17 KB 17 KB |
98ms
98ms |
Image
image/webp |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
OPTIONS H2 |
200 |
event
connect.segmint.net/ Frame |
0 0 |
450ms
416ms |
Preflight
|
172.64.150.82 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
event
Show response
connect.segmint.net/ |
0 205 B |
108ms
107ms |
XHR
text/plain |
172.64.150.82 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
en1xxXxz6j
Show response
connect.segmint.net/iframe/doughnut/ Frame FC0E |
509 B 913 B |
494ms
455ms |
Document
text/html |
104.18.37.174 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
en1MgagnxyfbrM
Show response
connect.segmint.net/bearclaw/invoke/ |
2 KB 2 KB |
142ms
117ms |
XHR
application/json |
172.64.150.82 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H/1.1 |
204 No Content |
/
client-logger.salemove.com/ |
0 0 |
392ms
180ms |
Fetch
|
52.7.4.58 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
98bbe84f231946d48de4331d0f29217d.png
cdn.segmint.net/ |
22 KB 22 KB |
9ms
8ms |
Image
image/png |
99.84.152.44 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
cookie-mapper
maprtb.segmint.net/rtb/simpli-fi/ Frame FC0E Redirect Chain
|
43 B 157 B |
450ms
435ms |
Image
image/gif |
104.18.37.174 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
ec0a3730-0bdd-0139-387d-06abc14c0bc6
Show response
tag.simpli.fi/sifitag/ Frame FC0E |
0 447 B |
121ms
61ms |
Script
application/javascript |
35.204.89.238 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
200 |
log_event
Show response
www.youtube.com/youtubei/v1/ Frame 5C22 |
28 B 50 B |
20ms
17ms |
XHR
application/json |
142.251.151.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
favicon-32x32.png
www.thomastonsavingsbank.com/ |
2 KB 2 KB |
108ms
108ms |
Other
image/png |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
206 Partial Content |
24-THOM-391_Goal-Getter-Tool-Walkthrough-With-Music_FINAL-CUT_R1-V1.mp4
www.thomastonsavingsbank.com/application/files/8217/1941/2435/ |
98 KB 0 |
104ms
104ms |
Media
video/mp4 |
192.140.7.143 COCC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||










































Verdicts & Comments Add Verdict or Comment
40 JavaScript Window variables
These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.
object| 0 object| 1 object| dataLayer string| CCM_DISPATCHER_FILENAME number| CCM_CID boolean| CCM_EDIT_MODE boolean| CCM_ARRANGE_MODE string| CCM_IMAGE_PATH string| CCM_APPLICATION_URL string| CCM_REL string| CCM_ACTIVE_LOCALE boolean| CCM_USER_REGISTERED object| google_tag_manager object| google_tag_data string| fesdpid string| fesdpextid string| __ibaseUrl boolean| GTPX_DEBUG function| gtpx object| sm object| _0x36F6 string| vv_curHost object| octillionXMLHttp object| __SVGATOR_PLAYER__ object| $egmint object| klaroConfig number| uidEvent object| bootstrap function| Vue object| klaro object| webpackChunkworx_theme object| klaroCloseButton function| runKlaro function| onYouTubeIframeAPIReady object| webpackJsonpSalemoveVisitorApp object| scriptUrl object| ttPolicy object| YT object| YTConfig function| onYTReady14 Cookies
Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.
| Domain/Path | Expires | Name / Value | |||
|---|---|---|---|---|---|
| www.thomastonsavingsbank.com/ | 1969-12-31 23:59:59 |
Name: COCC_WebHosting Value: !p8AmfXBDsoEWlis522j4bCR7MeZEbGovgqdO84CoY1rNH55utfiUr7+Flo2YE8287Li/o2sRqiBWNiziE7MW9XunoMIVbE11a6U1QU4= |
|||
| www.thomastonsavingsbank.com/ | 1970-01-21 16:47:31 |
Name: vv_session_id Value: IQZmACXBM39p1thfU9m9urGXpOI9RPfAJhr6ieex4dmB90 |
|||
| www.thomastonsavingsbank.com/ | 1970-01-22 02:23:29 |
Name: vv_visitor_id Value: IQZmACXBM39p1thfU9m9urGXpOI9RPf |
|||
| api.glia.com/ | 1970-01-22 01:33:05 |
Name: visitor_session Value: eyJhbGciOiJFUzI1NiJ9.eyJpYXQiOjE3ODg0NDk3NjYsInZpc2l0b3JfaWQiOiIzOTg4Y2IzMC05YTgzLTRiZmUtYjg5Ny05ZjdiZWVhZGQwMDciLCJpc3MiOiJHbGlhIFNpdGUgVmlzaXRvciBDb25maWciLCJraWQiOiIzNDhjNThjNS02ZWViLTQxODAtODliNy03YzRkOGM2NmRjMjMifQ.H0OEx1ILxAtrXnx1oQCH0kYucZti0OXkCVIii5WLmLa8Wiyq4LJfrdqQd7vntrcjqb59TuMRJ-8lDRbVd_QbWA |
|||
| api.glia.com/ | 1970-01-22 01:33:05 |
Name: visitor_session_partitioned Value: eyJhbGciOiJFUzI1NiJ9.eyJpYXQiOjE3ODg0NDk3NjYsInZpc2l0b3JfaWQiOiIzOTg4Y2IzMC05YTgzLTRiZmUtYjg5Ny05ZjdiZWVhZGQwMDciLCJpc3MiOiJHbGlhIFNpdGUgVmlzaXRvciBDb25maWciLCJraWQiOiIzNDhjNThjNS02ZWViLTQxODAtODliNy03YzRkOGM2NmRjMjMifQ.H0OEx1ILxAtrXnx1oQCH0kYucZti0OXkCVIii5WLmLa8Wiyq4LJfrdqQd7vntrcjqb59TuMRJ-8lDRbVd_QbWA |
|||
| www.thomastonsavingsbank.com/ | 1969-12-31 23:59:59 |
Name: klaro Value: %7B%22analytics_storage%22%3Atrue%2C%22ad_storage%22%3Atrue%2C%22YouTube%22%3Atrue%2C%22ADA%22%3Atrue%2C%22Chat%22%3Atrue%2C%22functional_storage%22%3Atrue%7D |
|||
| .youtube.com/ | 1970-01-21 21:06:41 |
Name: __Secure-YNID Value: 21.YT=muMG6q8gil662tlpr306a4fS-iP3K-Yq9G6jrOVbdw9N3LPWJrVZKcyCR_OcxRg7fGeEvrY0ea2gPcLjIcEDALynPVmsSdp6qYsfKdPQFCHXOQCca3zIRKWQq7rsgZL7INAllorSOi96l3fNrbHd7QOXX8Uy0EcEkLo42KJ7sYGW0N8NynuzHhroyk1fwVMAnmayy7j7lRolO604nNRQe-G_2C7KBCiYnNY1C44zdu0dKODP9wCI1lUDHOMnb6jyAei0hsUeBFidScj5g76KSCX27IGSDZrOXlyo52lthXYmIHDhJPWf3l0U-na86uqZpYF1ZmoHjJFQi-AsJ6Z_Tw |
|||
| .youtube.com/ | 1969-12-31 23:59:59 |
Name: YSC Value: aJByvFT_BeU |
|||
| .youtube.com/ | 1970-01-21 21:06:41 |
Name: __Secure-ROLLOUT_TOKEN Value: CJn8jbTLgpXFARCgss3I3tKWAxigss3I3tKWAw%3D%3D |
|||
| .youtube.com/ | 1970-01-21 21:06:41 |
Name: VISITOR_INFO1_LIVE Value: ebMc_KxmTWE |
|||
| .youtube.com/ | 1970-01-21 21:06:41 |
Name: VISITOR_PRIVACY_METADATA Value: CgJERRIEEgAgTQ%3D%3D |
|||
| .segmint.net/ | 1970-01-21 16:47:31 |
Name: __cf_bm Value: lJdKTOKyIC8HcZRTQZrWchvJtSlSpD2eSJ52kLSENaI-1788449769.5005364-1.0.1.1-RCjLrQvYFHaTmf37Ow0eDr5PJQ8XOI__4nsjs6A1qc7O1gu5rfgThCNxZdYVckxVDS.k5fsOWmckLzK._CSExIxyGAiRYpmYS0bLWpDaOUYR_Nnmj4XfMNG6Ghe4isHS |
|||
| .segmint.net/ | 1970-01-22 02:23:29 |
Name: SegmintId Value: ffef8c0f621f49a19d64459b297822b5 |
|||
| .simpli.fi/ | 1970-01-22 01:34:32 |
Name: suid Value: 688A4B8077D640E688F4E7F665386691 |
6 Console Messages
A page may trigger messages to the console to be logged. These are often error messages about being unable to load a resource or execute a piece of JavaScript. Sometimes they also provide insight into the technology behind a website.
| Source | Level | URL Text |
|---|
Security Headers
This page lists any security headers set by the main page. If you want to understand what these mean and how to use them, head on over to this page
| Header | Value |
|---|---|
| Strict-Transport-Security | max-age=63072000; includeSubdomains; preload |
| X-Content-Type-Options | nosniff |
| X-Frame-Options | SAMEORIGIN |
| X-Xss-Protection | 1; mode=block |
Indicators
This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.
api.glia.com
api.salemove.com
arttrk.com
cdn.segmint.net
client-logger.salemove.com
connect.segmint.net
fe.sitedataprocessing.com
fonts.googleapis.com
fonts.gstatic.com
googleads.g.doubleclick.net
gt-pixel-prod.groundtruth.com
i.ytimg.com
jnn-pa.googleapis.com
libs.salemove.com
maprtb.segmint.net
p.typekit.net
pubsub.salemove.com
px.premion.com
static.doubleclick.net
tag.simpli.fi
thombank.net
um.simpli.fi
use.typekit.net
www.google.com
www.googletagmanager.com
www.thomastonsavingsbank.com
www.youtube.com
104.18.37.174
142.251.110.155
142.251.127.149
142.251.127.95
142.251.14.94
142.251.14.97
142.251.151.119
142.251.153.4
142.251.156.4
151.101.193.91
172.217.117.4
172.64.150.82
18.173.187.29
18.173.187.89
18.173.205.74
18.227.200.194
18.67.13.98
184.24.77.135
184.24.77.167
188.114.96.3
192.140.7.143
192.178.183.119
34.203.115.134
34.7.37.3
35.204.89.238
52.7.4.58
99.84.152.44
0196ba918613b787a6b5ad55d60974386c81dfb282fa793cb6eef54a91eb4505
0557f857bf176c8b725f227b80d1360bd38baabe837fb586d7b3b54f3d5538b7
081ce5fa2167e2cb3fd0cb754fc8020d72b9ab101ab41f0db69a9957e0615f7a
09d294e53b562437fdfc88f05931e694dca4758c6fd76a41a48a7ae089618428
0aa49cded6c89343a514ac6a5bdf368cc49b43193c968852fa56a9b82e25cb32
0b42d1fc12015fe54b5ef8fbbe5b3413790f036ab038bd21499a37f8d92ab0ad
0be2685845e7138063179adcb3fabe150e32d67d9fd045e4e717ec99bcf5122a
0d77310d5cf8e35408eb53dee1c440e5c008b768b866464d8418322ffb4d8d85
0e0f6979da6efabbeaf4db52c12e61385bf2655f6de65723b50e98d1c906d8fe
11ec04e3948e25a0d78d2f77c04940b8e38a086624ec36fa4605a2a69b133e94
17d9225539fa164700d30fe143c863f12f383be8bcdd72f1d0c5d21d8a566a13
1816d16c020f471dc9194a773db3e54c1fa80bd23ab8f0239a7979572dae2d70
19bba1870b73f756d681a6759b4e8b2c4b45ce6c51f169433892cb1e9b07966b
1c0ff118a4290c99f39c90abb38703a866e47251b23cca20266c69c812ccafeb
1d9ff738be2684cce586553b75b38f126a1f9fbd19ce5244b5bc6484f842852b
1f4513a435d6a3047d20a50c1e7d4263de42146c74be227f774b5e82e6357e75
20b535fa80c8189e3b87d1803038389960203a886d502bc2ef1857affc2f38d2
29f6197bad68283cc1ffb2b06578fd52dee6527e95fbcc4f57580764b201483e
2b59f19a1fe089d38df6aefb60182eca55c59d112f048d6f93fbde3a6f5a4f36
2ddfe1accc7075b21399a96d8c7ae26b0368cce38b5554355c8d7614f82acb2e
319b83ebb77723ff2eb222673ead9f7d9a424108424db5cd1b0de1b01ff94a43
337a9d5681431693412c17bcc3ec5b557de3acf965051b4f5bc8cac5e1ff0b08
367ceebb927f17f3b805d22a22b53695985d4fe1fe6ee105608c4b8dbbf1bbfd
39de2c2c9b835d28be47dc93977b61b2608bce93f3753d2b49f90c4ca6c4dc0f
3fc45eddf17a4b30b0be4ac69472a5568ed62b161e6f13c1d3815f11dc1e642f
40c97e0278519dd6e0c73e7e7d9e39eee93fe1d340c6a4b92d9b22dfccde9307
40f554d2276f783f99728a5ef03d568143cea470aaeff25195b0728621aaea01
431bd417b33f26fb84ba99a3b7e735fbb7d9a470daf82af2265750341dc35778
44136fa355b3678a1146ad16f7e8649e94fb4fc21fe77e8310c060f61caaff8a
44e4c58f74ce8ca4dae2afa8de11fbfb895169d71851287adfeb76391eb536e0
45ccf4671a6bc2d165be226f7df90df8a0cd5751d8c7f1e1126598069499bb36
46281456234014ceb2a79bff447245de0f76b8d803be0738972ed374c3206c5b
47996e69ca2f5c325f596eba766b9ac5aacad726c9cab33ca700ff48fbff2413
48bd38bad85c99d75a2766da380cd2f60baa009941c2ad02cab07fd3a83a7824
493aee45414eb49235710762a3305d5fcf1d52e1130acc7d4be59b63b257da46
4db3daeb3b00863ba34d97c10223476ade0783a347db8d2b8c11ee385de681d3
50266d38fd67228c23915aed742da72a274c689100080b58388a29243a795a90
50f9c8dafe3ba1c529d66c96020789a3728dd6d54d6cc346a359713cac7ff994
51ca196f49a33e79e7870ff88ebd2829a3f627a51e7d690986618f0e7ad2b52d
54caf41dccda93de1bd2a04e9866dc4ecf86d654bbda5e5ff1f27905dbbbe495
554579896aae06495086846333e49ed1914649861d76852a6c0261280a8f904f
585cd79060efd2faf8e39a11ce5ffaba2a64662c9e5eb02946b45c16d0b1b8c2
62f3f809487194fcc55a3ebd88811a604ae496027bb425d4ebd15d9ae1921945
66938062fe0424051e55d9e115b38e12a91a06ca86b003ed50ee939831addd1c
693d949d8c3fdc7fd4ace7c340b5f177a9f0c5be7bafee8bc93a7d88b7523d75
6a75f318712a20bf91e2caa1bac205d1370e391befeeaa7d32d21c8bed9be97c
717f6bb5f6cc69c444f54376a72dee0ca7968b2a12e7c9475247ec85c0e75a53
735fe988f8e191aa2fefae53ed98d797b14dc04e8c5d0f354f546f6b8e56c26c
76321686518ff4054f418806bdc591e1cbd3a45f2501a4c4f86293be7709c6f3
7e11c7b2901836f9922ca959251c72b5c9b71e1006bed3157611ba72d310aa5e
7e945b501470153dabc11f8962343f62361258a2fcaaa49f81fc3a79653a7ef9
8143c89675df71759a06c766c213c7d65f2b02a74c72cbf48a300e7de80ff37d
81f203f9111aa7b1cc08ee9d408ab21f068d310040e294ecd223afc848b2545e
832dbd199f70ade357e88a3f5d32920c8c63e69258dc173d3b261686320895db
8784401a34ce07dc6668d73ecbd6ec63a30f585046fe863da09cb73b58b31476
8ea8791754915a898a3100e63e32978a6d1763be6df8e73a39d3a90d691cdeef
90769e74819d3f810eda99dbaa4d5552d383eb874f115a7802ae353b842d9f3d
940f0432ddd6557475d2bfb924588c6be39ac09ae065dcd4f5b95c038a30b880
94df3afb42282227481c3a498ac430c7511be1f64f9b415bc96518ce54b2c2c8
9520018fa5d81f4e4dc9d06afb576f90cbbaba209cfcc6cb60e1464647f7890b
969f593aeb57793babd68570377a45cabca6578a692ddafea1bc547cb582725e
96e3e223db36f20082cbc5b5393a6c783c91cd0d52b4d338857e1c2abbc0deeb
97786aec520840b9d1d00a3e3e0e8d2e6dd066ac6285b1b82859ad37af6d5fb7
980754c980254c3bfb981b6b7bad8a6e5ecf308c609c6a4eeeb39c4c21f7cc64
9807e3772196916b614d2d3d385373ba78ff5c5c26f69ffbdf827086667ee699
9834b82ad26e2a37583d22676a12dd2eb0fe7c80356a2114d0db1aa8b3899537
a065920df8cc4016d67c3a464be90099c9d28ffe7c9e6ee3a18f257efc58cbd7
a0b1be2fc1b00152555005cf48c940cd43cf3b442e08963662be11fc6beb84da
a3788bee4730a687f02c494947dd8d6b1022d247a97f3c8c2713863d6ef7f226
a3e0bf7c2555543edcad1dcf23f94f1a44d1c191a07bd47bdfced129c05cc21d
a3e2fa2e70283d4a004c9bf60c4566381ed6e69be9586927dacb8c78291df547
a439ed49621f98d07f3310151530ac76793ef5586094ccfc13389cbb99c7624b
af038292dbde728ac79b9dc7de00e17b1e1887f218506d3696c022f588b39c3b
b037df960b6f8e902033c963d7d75b93d3a48b7ebe2ceb6df19b6f4ef1a33bd1
b0ecffe23b67919c542c265dbdb9874b6236aadd2266ed5dd1e9694d00bc5d29
b3196ec6664220ff41ee2788d53dee5818e98adf73271a4da73404cd07c049b7
b7415938e5f777833eaa520879b32cf678c9913b806789992514892486531fe3
b9a479062e65b36551a61818edf8721136013bef72f9c07463dbc08348ff5085
be471bcc345ecfea5e9530062d5a52335e5127deff11168f0f71a327569eaded
be59e29b81aa8dce2b8a6db25bacbac4530e172a5c91de9a1260099030f76594
c067f70fd4d2e09312db7bd2c0f70e400b742e48d7e6483a0fd895de764d701a
c162e0079d40fe0a7c442a915b9de9b194b28215fb42816653b7c11bd747c8de
c1cd31fc875f823132779bdb93df4f02aaac34a052f0bdb1a1c347e31c76d9e1
c2dcf46501a48a87a7859596834012e81569a181f7b80bda4d91b04798f84751
c50225162c6e74e066c1017dfaa272f583440c1dc8755d4ceb7c2e446149cc1a
c8509e9d0075fd5f80dc38ef35c622464277a85bc1ec64b01418c45191a61c05
d1e9ddc813c3a470e6b94ad53a0a3aefcf2537e7415ec0eb9f72c51c9ec1cc5b
d601f229247b261d18181988f7337b3f652165187f3c22a109821a50ea96a0f9
d692a67352a3dfa80010c86a62761cfff05c0b1086618106a8576cc45a6a8115
d7d5e54ad1e33d7ab49c664323ced79cb9723ff15e9764cd0edc3e15208e8336
db6afae1f1f788136d46bf47264040087ca718ea32747b549d98f05703f4ba0e
e10ca2522b4345474dc519b4528efa0ba6e3d4eab2550e4e1a7bd064bdfe5312
e122fd434c3d1c9b5f176fb559280592ee35d4f7ec6add5da6f40f462838797a
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
e810ff4aa0e914aae17f40c3cb505df1abb51b4150edad59f7c9de86e6135b21
eb14baeac955bb11e33cd7fd3fd2f698cf20db1b450325f45ea843b6cdc82366
eed0dc1fdb5d97ed188ae16fd5e1024a5bb744af47340346be2146300a6c54b9
f2269282b00cfc88066d49a1136932bc518e826f86998fa5cbdbfcdcce2f2369
f43924d17d9391d302e458e0f2bb6af70ec81dfe557b2d70eb23948c1e8a8c6d
fc5874aa381a6113563d1599a0f93978999beb2c265c43acd7e718ce7284b53b
ff97e63d3eedfee5a1fc23981cfed610f4825b160336f0d816b3b66795cd9d29