
myfreemoney.app
172.67.139.233
Public Scan
Open in
urlscan Pro
https://myfreemoney.app/ 5mo old
Effective URL:
https://myfreemoney.app/freemoney 5mo old
Submission: On September 05 via automatic, source certstream-suspicious (September 5th 2026, 11:53:38 am UTC) — Scanned from US Go Pro
Only in urlscan Pro
- Select different country locations for Private Scans.
- Use a global network of additional scanning locations and residential IPs for scanning.
- Interact with pages while you are scanning them.
- Download files from remote websites.
- Scan websites on the Tor Network.
Summary
TLS certificate: Issued by YE1 on September 5th 2026. Valid for: 3mo.
This is the only time myfreemoney.app was scanned on urlscan.io!
urlscan.io Verdict: No classification
Domain & IP information
| IP Address | AS Autonomous System | ||
|---|---|---|---|
| 1 19 | 172.67.139.233 172.67.139.233 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 2 | 151.101.66.208 151.101.66.208 | 54113 (FASTLY) (FASTLY - Fastly) | |
| 3 | 23.12.147.52 23.12.147.52 | 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.) | |
| 5 | 3.167.37.89 3.167.37.89 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 1 | 104.16.79.73 104.16.79.73 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 25 25 | 142.251.153.119 142.251.153.119 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 8 | 173.194.44.147 173.194.44.147 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 9 | 192.178.155.103 192.178.155.103 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 2 | 172.253.115.103 172.253.115.103 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 6 | 172.253.147.99 172.253.147.99 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 54 | 10 |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| myfreemoney.app 5mo old |
ASN54113 (FASTLY - Fastly, Inc., US)
| content-images.thekrazycouponlady.com 4yr old |
ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL)
PTR: a23-12-147-52.deploy.static.akamaitechnologies.com
| images.thdstatic.com 6yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-3-167-37-89.iad61.r.cloudfront.net
| img.logo.dev 3yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| static.cloudflareinsights.com 7yr old |
ASN15169 (GOOGLE - Google LLC, US)
| www.google.com 14yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: yuchspe-in-f147.1e100.net
| t2.gstatic.com 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: yuiadrs-in-f103.1e100.net
| t1.gstatic.com 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: bg-in-f103.1e100.net
| t3.gstatic.com 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: yuchstz-in-f99.1e100.net
| t0.gstatic.com 10yr old |
| Apex Domain Subdomains |
Transfer | |
|---|---|---|
| 25 |
gstatic.com
t2.gstatic.com — Cisco Umbrella Rank: 2610 10yr old t1.gstatic.com — Cisco Umbrella Rank: 2620 10yr old t3.gstatic.com — Cisco Umbrella Rank: 2857 10yr old t0.gstatic.com — Cisco Umbrella Rank: 1700 10yr old |
80 KB |
| 25 |
google.com
25 redirects
www.google.com — Cisco Umbrella Rank: 3 14yr old |
451 B |
| 19 |
myfreemoney.app
1 redirects
myfreemoney.app 5mo old |
285 KB |
| 5 |
logo.dev
img.logo.dev — Cisco Umbrella Rank: 58709 3yr old |
116 KB |
| 3 |
thdstatic.com
images.thdstatic.com — Cisco Umbrella Rank: 17038 6yr old |
14 KB |
| 2 |
thekrazycouponlady.com
content-images.thekrazycouponlady.com — Cisco Umbrella Rank: 261633 4yr old |
25 KB |
| 1 |
cloudflareinsights.com
static.cloudflareinsights.com — Cisco Umbrella Rank: 308 7yr old |
10 KB |
| 54 | 7 |
| Domain | Requested by | |
|---|---|---|
| 25 | www.google.com | 25 redirects |
| 19 | myfreemoney.app |
1 redirects
myfreemoney.app
static.cloudflareinsights.com |
| 9 | t1.gstatic.com |
myfreemoney.app
|
| 8 | t2.gstatic.com |
myfreemoney.app
|
| 6 | t0.gstatic.com |
myfreemoney.app
|
| 5 | img.logo.dev |
myfreemoney.app
|
| 3 | images.thdstatic.com |
myfreemoney.app
|
| 2 | t3.gstatic.com |
myfreemoney.app
|
| 2 | content-images.thekrazycouponlady.com |
myfreemoney.app
|
| 1 | static.cloudflareinsights.com |
myfreemoney.app
|
| 54 | 10 |
This site contains links to these domains. Also see Links.
| Subject Issuer | Validity | Valid | |
|---|---|---|---|
| myfreemoney.app YE1 |
2026-09-05 - 2026-12-04 |
3mo | crt.sh |
| content-images.thekrazycouponlady.com Certainly Intermediate R1 |
2026-08-24 - 2026-09-23 |
1mo | crt.sh |
| www.homedepot.com DigiCert Global G3 TLS ECC SHA384 2020 CA1 |
2026-07-27 - 2027-02-10 |
7mo | crt.sh |
| img.logo.dev Amazon RSA 2048 M01 |
2025-11-27 - 2026-12-26 |
1yr | crt.sh |
| cloudflareinsights.com WE1 |
2026-08-14 - 2026-11-12 |
3mo | crt.sh |
This page contains 1 frames:
Primary Page:
https://myfreemoney.app/freemoney
Frame ID: 1DE738D1C3E3BF033E90AFB8563CF364
Requests: 55 HTTP requests in this frame
Screenshot
Go Pro
Only in urlscan Pro
Use the Visual Search feature to find pages with visually similar screenshots.
Click for more information
Free trials of urlscan Pro are available.
Page Title
My Free LifePage URL History
Go Pro
Only in urlscan Pro
Search our real-time database of newly observed domains and
hostnames. Pivot on different attributes, and setup keyword alerts for
newly observed domains.
Click for more information
Free trials of urlscan Pro are available.
Show full URLs
-
https://myfreemoney.app/
HTTP 302
https://myfreemoney.app/freemoney Page URL
Detected technologies
 Cloudflare Browser Insights
(Analytics)
Expand
Detected patterns
- static\.cloudflareinsights\.com/beacon(?:\.min)?\.js
Page Statistics
19 Outgoing links
Go Pro
Only in urlscan Pro
Effortlessly use any on-page link as a pivot to discover other pages pointing to the exact same destination. Seamlessly trace both specific URLs and broader domains to uncover hidden connection networks and map out backlink relationships with ease.
Click for more information
Free trials of urlscan Pro are available.
These are links going to different origins than the main page.
Title: Free Dollar General FREE Neutrogena Collagen Bank Moisturizer at Dollar General See details ›
Search URL Search Domain Scan URL
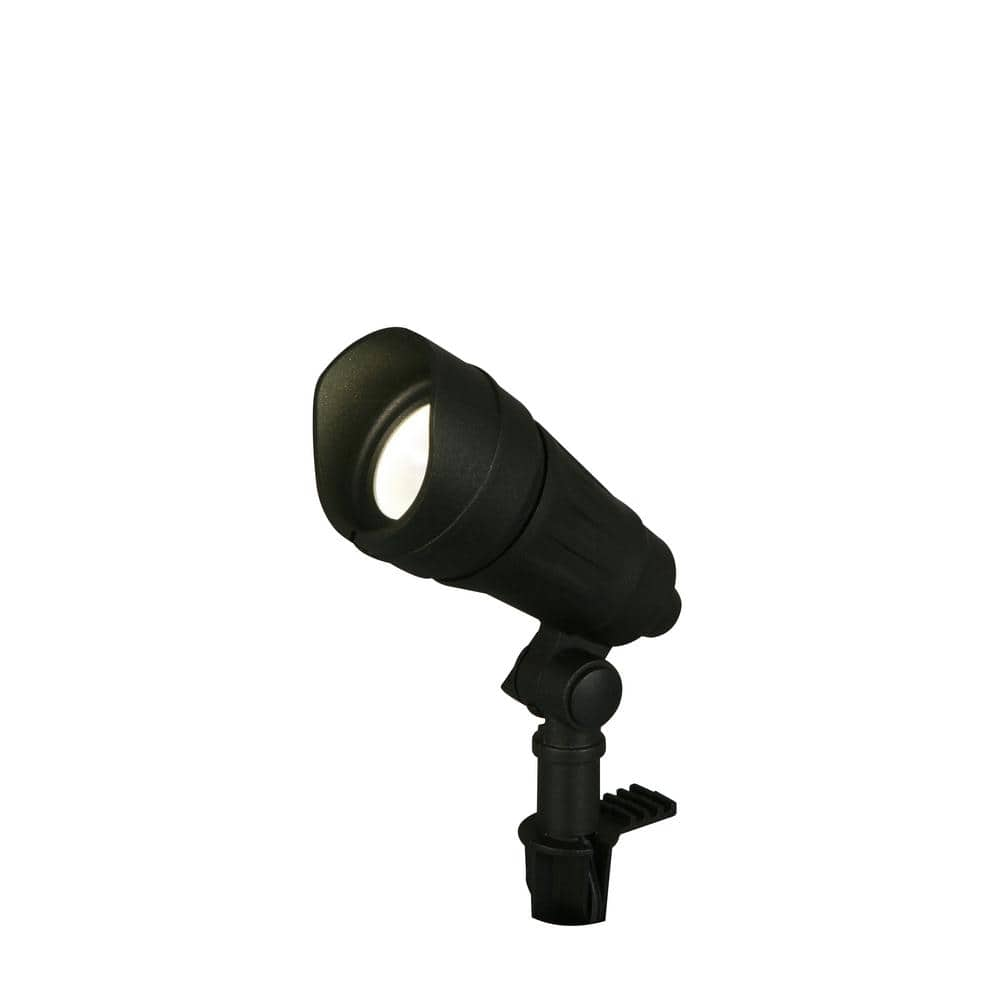
Title: $0.01 Hampton Bay Hampton Bay 400 Lumen Low Voltage Black Integrated LED Outdoor Spotlight See details ›
Search URL Search Domain Scan URL
Title: Free Amazon Amazon Prime Student — 6-Month FREE Trial See details ›
Search URL Search Domain Scan URL
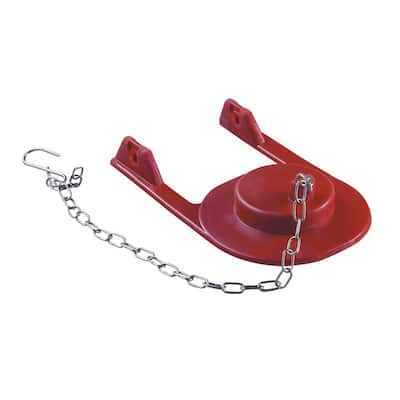
Title: $0.01 KOHLER Rialto 2 in. Toilet Tank Flapper See details ›
Search URL Search Domain Scan URL
Title: Free Target FREE Pampers Amore Diapers at Target See details ›
Search URL Search Domain Scan URL
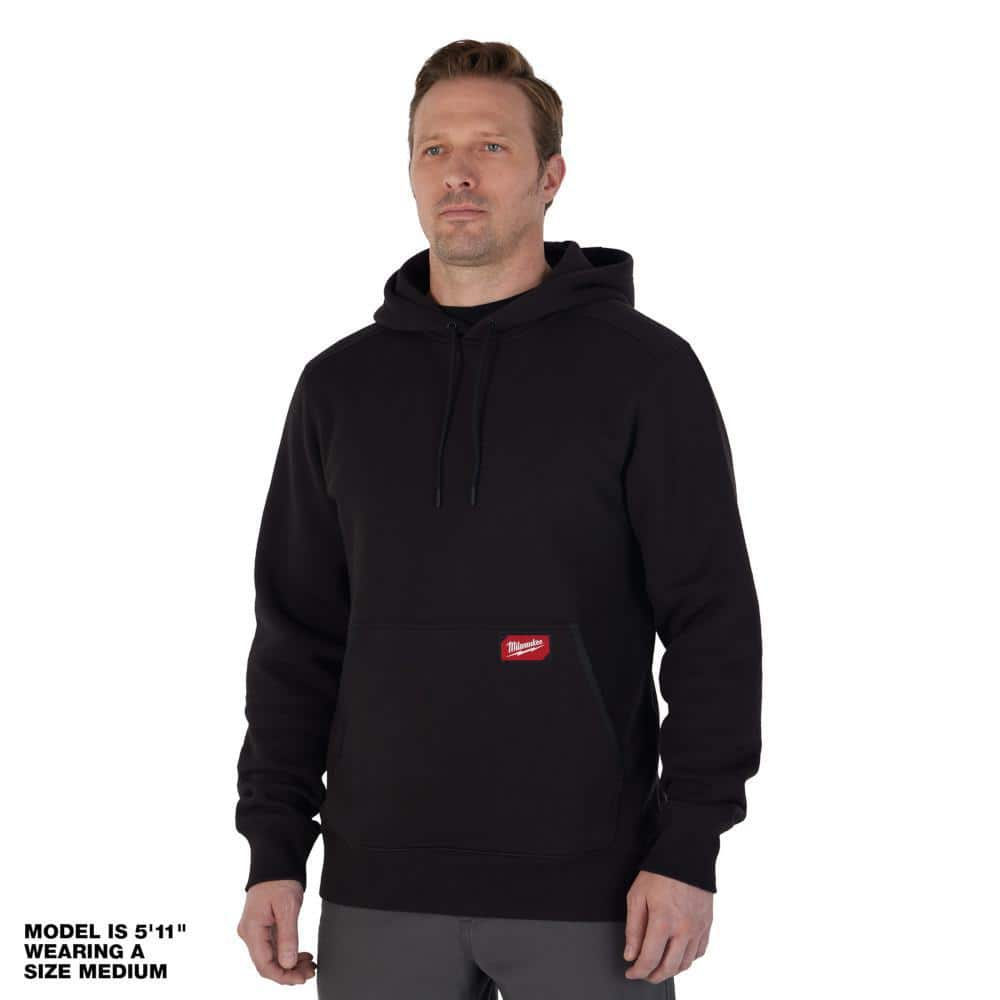
Title: $0.01 Milwaukee Men's Large Black Midweight Cotton/Polyester Long-Sleeve Pullover Hoodie See details ›
Search URL Search Domain Scan URL
Title: Craigslist — FreeCurb alerts & giveawaysOpen →
Search URL Search Domain Scan URL
Title: Facebook MarketplaceFree items near youOpen →
Search URL Search Domain Scan URL
Title: OfferUpFree & cheap local findsOpen →
Search URL Search Domain Scan URL
Title: FreecycleGive & get, totally freeOpen →
Search URL Search Domain Scan URL
Title: Buy NothingNeighborhood gift economyOpen →
Search URL Search Domain Scan URL
Title: NextdoorFree finds from neighborsOpen →
Search URL Search Domain Scan URL
Title: GSA AuctionsFederal surplus — cars, electronics, jewelryOpen →
Search URL Search Domain Scan URL
Title: GovDealsState & local government surplusOpen →
Search URL Search Domain Scan URL
Title: Public SurplusAgency surplus auctionsOpen →
Search URL Search Domain Scan URL
Title: U.S. Treasury AuctionsSeized property & real estateOpen →
Search URL Search Domain Scan URL
Title: HUD HomesForeclosed homes, often cheapOpen →
Search URL Search Domain Scan URL
Title: PropertyRoomPolice-seized goodsOpen →
Search URL Search Domain Scan URL
Title: All Federal AuctionsThe full government listOpen →
Search URL Search Domain Scan URL
Page URL History
This captures the URL locations of the websites, including HTTP redirects and client-side redirects via JavaScript or Meta fields.
-
https://myfreemoney.app/
HTTP 302
https://myfreemoney.app/freemoney Page URL
Redirected requests
There were HTTP redirect chains for the following requests:
Request Chain 22- https://www.google.com/s2/favicons?domain=craigslist.org&sz=256 HTTP 301
- https://t2.gstatic.com/faviconV2?client=SOCIAL&type=FAVICON&fallback_opts=TYPE,SIZE,URL&url=http://craigslist.org&size=256
- https://www.google.com/s2/favicons?domain=facebook.com&sz=256 HTTP 301
- https://t2.gstatic.com/faviconV2?client=SOCIAL&type=FAVICON&fallback_opts=TYPE,SIZE,URL&url=http://facebook.com&size=256
- https://www.google.com/s2/favicons?domain=offerup.com&sz=256 HTTP 301
- https://t1.gstatic.com/faviconV2?client=SOCIAL&type=FAVICON&fallback_opts=TYPE,SIZE,URL&url=http://offerup.com&size=256
- https://www.google.com/s2/favicons?domain=freecycle.org&sz=256 HTTP 301
- https://t3.gstatic.com/faviconV2?client=SOCIAL&type=FAVICON&fallback_opts=TYPE,SIZE,URL&url=http://freecycle.org&size=256
- https://www.google.com/s2/favicons?domain=buynothingproject.org&sz=256 HTTP 301
- https://t1.gstatic.com/faviconV2?client=SOCIAL&type=FAVICON&fallback_opts=TYPE,SIZE,URL&url=http://buynothingproject.org&size=256
- https://www.google.com/s2/favicons?domain=nextdoor.com&sz=256 HTTP 301
- https://t3.gstatic.com/faviconV2?client=SOCIAL&type=FAVICON&fallback_opts=TYPE,SIZE,URL&url=http://nextdoor.com&size=256
- https://www.google.com/s2/favicons?domain=gsaauctions.gov&sz=256 HTTP 301
- https://t2.gstatic.com/faviconV2?client=SOCIAL&type=FAVICON&fallback_opts=TYPE,SIZE,URL&url=http://gsaauctions.gov&size=256
- https://www.google.com/s2/favicons?domain=govdeals.com&sz=256 HTTP 301
- https://t1.gstatic.com/faviconV2?client=SOCIAL&type=FAVICON&fallback_opts=TYPE,SIZE,URL&url=http://govdeals.com&size=256
- https://www.google.com/s2/favicons?domain=publicsurplus.com&sz=256 HTTP 301
- https://t0.gstatic.com/faviconV2?client=SOCIAL&type=FAVICON&fallback_opts=TYPE,SIZE,URL&url=http://publicsurplus.com&size=256
- https://www.google.com/s2/favicons?domain=treasury.gov&sz=256 HTTP 301
- https://t1.gstatic.com/faviconV2?client=SOCIAL&type=FAVICON&fallback_opts=TYPE,SIZE,URL&url=http://treasury.gov&size=256
- https://www.google.com/s2/favicons?domain=hudhomestore.gov&sz=256 HTTP 301
- https://t2.gstatic.com/faviconV2?client=SOCIAL&type=FAVICON&fallback_opts=TYPE,SIZE,URL&url=http://hudhomestore.gov&size=256
- https://www.google.com/s2/favicons?domain=propertyroom.com&sz=256 HTTP 301
- https://t1.gstatic.com/faviconV2?client=SOCIAL&type=FAVICON&fallback_opts=TYPE,SIZE,URL&url=http://propertyroom.com&size=256
- https://www.google.com/s2/favicons?domain=usa.gov&sz=256 HTTP 301
- https://t2.gstatic.com/faviconV2?client=SOCIAL&type=FAVICON&fallback_opts=TYPE,SIZE,URL&url=http://usa.gov&size=256
- https://www.google.com/s2/favicons?domain=bjsrestaurants.com&sz=256 HTTP 301
- https://t1.gstatic.com/faviconV2?client=SOCIAL&type=FAVICON&fallback_opts=TYPE,SIZE,URL&url=http://bjsrestaurants.com&size=256
- https://www.google.com/s2/favicons?domain=on.ltk.com&sz=256 HTTP 301
- https://t0.gstatic.com/faviconV2?client=SOCIAL&type=FAVICON&fallback_opts=TYPE,SIZE,URL&url=http://on.ltk.com&size=256
- https://www.google.com/s2/favicons?domain=shoplowes.me&sz=256 HTTP 301
- https://t2.gstatic.com/faviconV2?client=SOCIAL&type=FAVICON&fallback_opts=TYPE,SIZE,URL&url=http://shoplowes.me&size=256
- https://www.google.com/s2/favicons?domain=ediblearrangements.com&sz=256 HTTP 301
- https://t2.gstatic.com/faviconV2?client=SOCIAL&type=FAVICON&fallback_opts=TYPE,SIZE,URL&url=http://ediblearrangements.com&size=256
- https://www.google.com/s2/favicons?domain=tiktok.com&sz=256 HTTP 301
- https://t0.gstatic.com/faviconV2?client=SOCIAL&type=FAVICON&fallback_opts=TYPE,SIZE,URL&url=http://tiktok.com&size=256
- https://www.google.com/s2/favicons?domain=si.edu&sz=256 HTTP 301
- https://t0.gstatic.com/faviconV2?client=SOCIAL&type=FAVICON&fallback_opts=TYPE,SIZE,URL&url=http://si.edu&size=256
- https://www.google.com/s2/favicons?domain=evgo.com&sz=256 HTTP 301
- https://t1.gstatic.com/faviconV2?client=SOCIAL&type=FAVICON&fallback_opts=TYPE,SIZE,URL&url=http://evgo.com&size=256
- https://www.google.com/s2/favicons?domain=rei.com&sz=256 HTTP 301
- https://t0.gstatic.com/faviconV2?client=SOCIAL&type=FAVICON&fallback_opts=TYPE,SIZE,URL&url=http://rei.com&size=256
- https://www.google.com/s2/favicons?domain=goto.target.com&sz=256 HTTP 301
- https://t1.gstatic.com/faviconV2?client=SOCIAL&type=FAVICON&fallback_opts=TYPE,SIZE,URL&url=http://goto.target.com&size=256
- https://www.google.com/s2/favicons?domain=tryazon.com&sz=256 HTTP 301
- https://t1.gstatic.com/faviconV2?client=SOCIAL&type=FAVICON&fallback_opts=TYPE,SIZE,URL&url=http://tryazon.com&size=256
- https://www.google.com/s2/favicons?domain=sheerid.com&sz=256 HTTP 301
- https://t2.gstatic.com/faviconV2?client=SOCIAL&type=FAVICON&fallback_opts=TYPE,SIZE,URL&url=http://sheerid.com&size=256
- https://www.google.com/s2/favicons?domain=tubbytodd.com&sz=256 HTTP 301
- https://t0.gstatic.com/faviconV2?client=SOCIAL&type=FAVICON&fallback_opts=TYPE,SIZE,URL&url=http://tubbytodd.com&size=256
54 HTTP transactions
Go Pro
Only in urlscan Pro
Inspect WebSocket connections, examine POST data effortlessly, and track overlap counts in real time. Features live search and filtering across all HTTP output, complete with full response metadata for deep analysis.
Click for more information
Free trials of urlscan Pro are available.
1 data transactions
| Method Protocol |
Status | Resource Path |
Size x-fer |
Time Latency |
Type MIME-Type |
IP Location |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
|
GET H3 |
200 |
Primary Request
freemoney
Show response
myfreemoney.app/ Redirect Chain
|
162 KB 47 KB |
246ms
245ms |
Document
text/html |
172.67.139.233 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
fonts.css
myfreemoney.app/static/ |
1 KB 1 KB |
259ms
258ms |
Stylesheet
text/css |
172.67.139.233 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
image
content-images.thekrazycouponlady.com/nie44ndm9bqr/4CWlgsfGVaLMFbeGstez2U/d1df701558e8dfcfe5c19b71760ac478/ |
14 KB 14 KB |
917ms
285ms |
Image
image/avif |
151.101.66.208 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
millennium-black-hampton-bay-landscape-flood-spot-lights-iwh2301ll-7-64_1000.jpg
images.thdstatic.com/productImages/3f1d5668-fc31-4def-b4a3-87ed01c45e8d/svn/ |
3 KB 3 KB |
862ms
209ms |
Image
image/avif |
23.12.147.52 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
amazon.com
img.logo.dev/ |
26 KB 26 KB |
1044ms
400ms |
Image
image/png |
3.167.37.89 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
kohler-toilet-flappers-gp83064-64_400.jpg
images.thdstatic.com/productImages/5a2d3638-3508-45cd-8126-0e37541757a3/svn/ |
3 KB 3 KB |
862ms
219ms |
Image
image/avif |
23.12.147.52 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
image
content-images.thekrazycouponlady.com/nie44ndm9bqr/JO6XLI8WtOc3XUIo6Jnc6/7539e937d4aee680ba4cc261e28b9147/ |
10 KB 11 KB |
732ms
110ms |
Image
image/avif |
151.101.66.208 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
milwaukee-hoodies-sweatshirts-351b-l-64_1000.jpg
images.thdstatic.com/productImages/71ff90e3-4dce-4648-8d4d-f9aefbd5eed3/svn/ |
7 KB 7 KB |
1074ms
431ms |
Image
image/avif |
23.12.147.52 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
welcome_settlements.jpg
myfreemoney.app/static/img/ |
65 KB 66 KB |
272ms
271ms |
Image
image/jpeg |
172.67.139.233 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
v31edd6df95cf4e85bb4c19e7a9bdbcba1788362987495
Show response
static.cloudflareinsights.com/beacon.min.js/ |
30 KB 10 KB |
703ms
73ms |
Script
text/javascript |
104.16.79.73 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET DATA |
200 OK |
truncated
/ |
260 B 0 |
Image
image/svg+xml |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
inter.woff2
myfreemoney.app/static/fonts/ |
47 KB 48 KB |
300ms
299ms |
Font
application/octet-stream |
172.67.139.233 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
home-feed
Show response
myfreemoney.app/api/freemoney/ |
156 KB 28 KB |
216ms
215ms |
Fetch
application/json |
172.67.139.233 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
home-feed
Show response
myfreemoney.app/api/freemoney/ |
83 KB 12 KB |
238ms
235ms |
Fetch
application/json |
172.67.139.233 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
home-feed
Show response
myfreemoney.app/api/freemoney/ |
110 KB 18 KB |
192ms
190ms |
Fetch
application/json |
172.67.139.233 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
home-feed
Show response
myfreemoney.app/api/freemoney/ |
6 KB 2 KB |
247ms
245ms |
Fetch
application/json |
172.67.139.233 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
penny-list
Show response
myfreemoney.app/api/freemoney/ |
106 KB 28 KB |
216ms
214ms |
Fetch
application/json |
172.67.139.233 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
home-feed
Show response
myfreemoney.app/api/freemoney/ |
34 KB 9 KB |
196ms
194ms |
Fetch
application/json |
172.67.139.233 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
home-feed
Show response
myfreemoney.app/api/freemoney/ |
59 KB 8 KB |
200ms
198ms |
Fetch
application/json |
172.67.139.233 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
home-feed
Show response
myfreemoney.app/api/freemoney/ |
2 KB 1 KB |
176ms
174ms |
Fetch
application/json |
172.67.139.233 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
home-feed
Show response
myfreemoney.app/api/freemoney/ |
4 KB 2 KB |
179ms
178ms |
Fetch
application/json |
172.67.139.233 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
home-feed
Show response
myfreemoney.app/api/freemoney/ |
34 KB 9 KB |
367ms
174ms |
Fetch
application/json |
172.67.139.233 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
pro-status
Show response
myfreemoney.app/api/freemoney/ |
25 B 759 B |
185ms
184ms |
Fetch
application/json |
172.67.139.233 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
faviconV2
t2.gstatic.com/ Redirect Chain
|
2 KB 2 KB |
1235ms
141ms |
Image
image/png |
173.194.44.147 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
faviconV2
t2.gstatic.com/ Redirect Chain
|
8 KB 8 KB |
1234ms
135ms |
Image
image/png |
173.194.44.147 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
faviconV2
t1.gstatic.com/ Redirect Chain
|
4 KB 5 KB |
1291ms
135ms |
Image
image/png |
192.178.155.103 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
faviconV2
t3.gstatic.com/ Redirect Chain
|
2 KB 2 KB |
1354ms
197ms |
Image
image/png |
172.253.115.103 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
faviconV2
t1.gstatic.com/ Redirect Chain
|
2 KB 2 KB |
1195ms
140ms |
Image
image/png |
192.178.155.103 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
faviconV2
t3.gstatic.com/ Redirect Chain
|
3 KB 4 KB |
1250ms
196ms |
Image
image/png |
172.253.115.103 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
faviconV2
t2.gstatic.com/ Redirect Chain
|
164 B 285 B |
1190ms
203ms |
Image
image/png |
173.194.44.147 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
faviconV2
t1.gstatic.com/ Redirect Chain
|
308 B 439 B |
1192ms
137ms |
Image
image/png |
192.178.155.103 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
faviconV2
t0.gstatic.com/ Redirect Chain
|
171 B 723 B |
1192ms
140ms |
Image
image/png |
172.253.147.99 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
faviconV2
t1.gstatic.com/ Redirect Chain
|
333 B 452 B |
1246ms
195ms |
Image
image/png |
192.178.155.103 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
404 |
faviconV2
t2.gstatic.com/ Redirect Chain
|
726 B 790 B |
1216ms
228ms |
Image
image/png |
173.194.44.147 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
faviconV2
t1.gstatic.com/ Redirect Chain
|
488 B 601 B |
1256ms
204ms |
Image
image/png |
192.178.155.103 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
faviconV2
t2.gstatic.com/ Redirect Chain
|
1 KB 2 KB |
1133ms
142ms |
Image
image/png |
173.194.44.147 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
panerabread.com
img.logo.dev/ |
26 KB 26 KB |
331ms
329ms |
Image
image/png |
3.167.37.89 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
ihop.com
img.logo.dev/ |
27 KB 27 KB |
263ms
262ms |
Image
image/png |
3.167.37.89 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
tacobell.com
img.logo.dev/ |
14 KB 14 KB |
391ms
390ms |
Image
image/png |
3.167.37.89 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
bk.com
img.logo.dev/ |
22 KB 22 KB |
402ms
401ms |
Image
image/png |
3.167.37.89 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
200 |
auto-restore
Show response
myfreemoney.app/api/freemoney/ |
25 B 758 B |
170ms
169ms |
Fetch
application/json |
172.67.139.233 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
faviconV2
t1.gstatic.com/ Redirect Chain
|
3 KB 3 KB |
1003ms
196ms |
Image
image/png |
192.178.155.103 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
404 |
faviconV2
t0.gstatic.com/ Redirect Chain
|
726 B 790 B |
1007ms
202ms |
Image
image/png |
172.253.147.99 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
faviconV2
t2.gstatic.com/ Redirect Chain
|
234 B 345 B |
999ms
256ms |
Image
image/png |
173.194.44.147 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
faviconV2
t2.gstatic.com/ Redirect Chain
|
13 KB 13 KB |
947ms
206ms |
Image
image/png |
173.194.44.147 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
faviconV2
t0.gstatic.com/ Redirect Chain
|
953 B 1 KB |
1008ms
208ms |
Image
image/png |
172.253.147.99 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
faviconV2
t0.gstatic.com/ Redirect Chain
|
20 KB 20 KB |
947ms
141ms |
Image
image/png |
172.253.147.99 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
faviconV2
t1.gstatic.com/ Redirect Chain
|
3 KB 3 KB |
1004ms
199ms |
Image
image/png |
192.178.155.103 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
faviconV2
t0.gstatic.com/ Redirect Chain
|
4 KB 4 KB |
1009ms
208ms |
Image
image/png |
172.253.147.99 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
404 |
faviconV2
t1.gstatic.com/ Redirect Chain
|
726 B 790 B |
1052ms
251ms |
Image
image/png |
192.178.155.103 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
faviconV2
t1.gstatic.com/ Redirect Chain
|
302 B 433 B |
1056ms
251ms |
Image
image/png |
192.178.155.103 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
faviconV2
t2.gstatic.com/ Redirect Chain
|
3 KB 3 KB |
940ms
202ms |
Image
image/png |
173.194.44.147 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
faviconV2
t0.gstatic.com/ Redirect Chain
|
3 KB 3 KB |
1015ms
214ms |
Image
image/png |
172.253.147.99 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
204 |
rum
Show response
myfreemoney.app/cdn-cgi/ |
0 451 B |
71ms
70ms |
XHR
text/plain |
172.67.139.233 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
icon-192.png
myfreemoney.app/static/ |
2 KB 2 KB |
264ms
264ms |
Other
image/png |
172.67.139.233 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||








Verdicts & Comments Add Verdict or Comment
95 JavaScript Window variables
Go Pro
Only in urlscan Pro
Inspect and pivot on JavaScript variables, identifiers, and other key site metadata data with urlscan Pro. Reveal and search on client-side frameworks, runtime variables, and custom values.
Click for more information
Free trials of urlscan Pro are available.
These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.
function| thumb function| art object| homeList object| PILL_CAT function| feedCard number| MENU_CHUNK number| menuShown function| renderMenu function| renderFeatured function| locState function| loadHomeFeed object| SHELF object| CAT_LABEL object| ACTION object| SAVE_VERB function| actionFor function| saveVerbFor function| shelfCard function| renderShelf function| loadHomeShelves object| HERO function| renderHero function| itemKey function| updateCart function| saveToList function| renderList object| PENNY_ITEMS string| PENNY_SORT function| pennyVal function| pennyProduct function| renderPenny function| loadPenny object| CAL_ALL object| CL_STATE object| CL_CITY object| STATE_ABBR function| clUrl function| loadLoc function| saveLoc function| renderFree function| escH function| timeAgo boolean| redditLoaded function| loadReddit boolean| recallsLoaded function| loadRecalls object| GOV object| FOOD function| renderFood function| openFoodDetail function| closeFoodDetail function| route function| go function| openMenu function| closeMenu function| toast object| dsave object| FM_JSON_HEADERS function| isSafeUrl function| startCheckout object| pcta object| pyr function| snSearch object| snGo function| applyPro function| checkProStatus function| rsErrMsg function| rsReset function| rsOpen function| rsClose function| rsSendCode function| rsConfirm function| fmManageSub object| rsBgEl object| askFab object| askBg object| askSheet object| askAns object| askInput object| askSend function| askOpen function| askClose function| askAnswer object| CUR_DETAIL function| openDetail function| swipeDown object| askX function| setZip object| MFL function| fmClearSearch function| fmQuick function| a2hsClose function| a2hsDoInstall object| __cfBeacon function| setPillCtx1 Cookies
Go Pro
Only in urlscan Pro
Review, search, and pivot on browser cookies and persistence site data to see how a site tracks users and keeps sessions alive across visits.
Click for more information
Free trials of urlscan Pro are available.
Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.
| Domain/Path | Expires | Name / Value | |||
|---|---|---|---|---|---|
| myfreemoney.app/ | 1970-01-21 17:33:21 |
Name: fm_mix Value: 518612469 |
3 Console Messages
A page may trigger messages to the console to be logged. These are often error messages about being unable to load a resource or execute a piece of JavaScript. Sometimes they also provide insight into the technology behind a website.
| Source | Level | URL Text |
|---|
Security Headers
This page lists any security headers set by the main page. If you want to understand what these mean and how to use them, head on over to this page
| Header | Value |
|---|---|
| Content-Security-Policy | default-src 'self'; script-src 'self' https://js.stripe.com 'unsafe-inline' https://static.cloudflareinsights.com; style-src 'self' 'unsafe-inline' https://fonts.googleapis.com; connect-src 'self' https://api.stripe.com https://checkout.stripe.com; frame-src https://js.stripe.com https://checkout.stripe.com; img-src 'self' data: https:; font-src 'self' https://fonts.gstatic.com; object-src 'none'; base-uri 'self'; form-action 'self' https://checkout.stripe.com; frame-ancestors 'none' |
| Strict-Transport-Security | max-age=31536000; includeSubDomains |
| X-Content-Type-Options | nosniff |
| X-Frame-Options | DENY |
Indicators
This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.
content-images.thekrazycouponlady.com
images.thdstatic.com
img.logo.dev
myfreemoney.app
static.cloudflareinsights.com
t0.gstatic.com
t1.gstatic.com
t2.gstatic.com
t3.gstatic.com
www.google.com
104.16.79.73
142.251.153.119
151.101.66.208
172.253.115.103
172.253.147.99
172.67.139.233
173.194.44.147
192.178.155.103
23.12.147.52
3.167.37.89
01c59b944a587228042b3df1d1222c504638414393110a47b0fb0bb1a9615c9d
08c4fd72f9d96a7aa554510dff2c293973b1b092dff1b9b282bce9111b50ef41
0cbda665f3b55979b986e46e666cbb0d77d98495873aad3704862e0d8341c666
0fbff0a46d8daa9f1898500db1dd85e4a7371ecc0c62fb53d13cde5283d23e98
111584929bc75033c104503d389e3a3c4be0bfcc22f49a5c4fadadd35ea403c5
11b5990b034c5b0c01a81e1842157e0338314b360ff2b4338f5107aac038ade6
1640ff6be9646d596c34946c9f0d02da9e821d3af154cc374c138a1a572dc76b
17da8da1b940981183585614182cfd79f3d44ceb1d4c2558fb20d489b617a82a
1dcb8e25178be93e2f38544eda3b04f90ed8551b1eb7d92f19b494bc61ea8b15
208684bc21568b6ba36443f3e99aaf9f4bb3b61e6a02852dac428d0c8b03e3ed
21c2738db874ac6e54f2217840a940b36d50a4e31faeaa2199b581167cdce002
2413f38aac580f6ead56f4101f44027daaee71db30f2d589ee71290b68d986bb
2b8d86d7e2e8a878cd52147b0291bef37dac618147fa92ce8c1ebe439f783288
2c2e3e13bc5ed0202b585b63436b5db0d4a82a57b26a76fe273b54613ba1a04c
3100e775e8616cd2611beecfa23a4263d7037586789b43f035236a2e6fbd4c62
32548167884992764b14ffebed9073cdb33562b51fcd5ae2402f262ae63553c5
3b7794ddfee49bc312a835f9901aa259a1bc0ea0c9e657761c6438b46850cb82
3bf2e6ebf24f8c95e652e30cbfee9763c28131eaf537de64545917929994ce00
3f09df0846f6576559eb171a67b012463f0b0ad7b8d17159ecb7beafcab8aa82
43ecccad754eb0640b00ebc3a590a54f6c4a260c752f94c5989dbd2ffbd0f41c
47140271b7015dd50c3ac08a05260a2ace92c324388d38a4b0fea453e7694de5
487dec04c049b96d57e8f391e6badc9c09d876fc46fd7f2b33bcd98542091dfd
5238a81948ea4101c8472c344648e9cc471f643e6de43289e066e233c9708c42
596f0cf77eabdab44b383983e51987817123eadf3d9c82c5619951fd4b8d0df0
59bfe9bc385ad69f50793ce4a53397316d7a875a7148a63c16df9b674c6cda64
6779bd723dc63e43f420709b6417223d9d6456818b301414c758b6978b32b10b
6f0b54a80372e7f7218376bb670c8742bcf28de5603c9a4478371d1f443d61f6
72076b2236f10d53f9d5518b9d3de1e571f680dc8387f4b2d239633d4e467614
7490d223ea885df3e3b360279ef8ae77eaa0159142f8f730552e9a875d44d5d6
896b3a09bd1b4b5d70577fdeed3571052867a131891c18b98381bb2af5939e9a
98f4915f9585430bdb1270f0666f377a0dacf8a18bc6acedc7e662fef47fc3c1
9c53dc0b8ebe22e162e6723a43130171645c7887bf37c305c5396a8a407c1628
a0f31901cc14b7b958d45a4e542acdee36f72e125c70efb339a72dd02836f170
afd53ffce1af577ccb35c58301f67f5ccde5e56b982366391e352b5870c70f8a
bc6d5cfcd555a32f3fd882fcc72b337a087fc0ac68421d83b1c57843fa143b37
c2ad24a9296c7cd0f8ecff4ad5abf41c6eb53632c86dd234e7f805082d07fe2c
d149903dbd50105cfa9bba2443c64907b617f23af06c18c1377b84326ec3c8a5
d2d547b5c1960f7e4206c818439c47645b02cdea35a73d8c5e1c918e4dfe4eb4
d5cac350345021b9f6aee314f0291c2a57748906abe29f82b05f22351b03b56f
d6c228c97236f5a6999992e0eb58ec9800e3778b17042d9ca3af89431a1c0a27
d6ea227bada247c95d5f4adb43bb85b4c198e8b677fbaad56e4adc819e80734e
de5bfffbcffd9c7057b9bf1aaa46ce31ba02bcebb01ad778a976c9aa3844de0b
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
e40547e421f1d7a6c541d3e1649869075463dea4f9bf66ec4c5fb78b4ad83658
e421a9daf1ebd712bab3febecb1f93b765fbfc2b22d2c3b4231efe3203de2381
e56f1d0bc7c9825814106f84dd21d883c316969ac368f7d9a5ce6075495850a1
e59a471671a1e5327cd1b8f9e01facba590d6c3d396da417cec9d5dd39abf3c2
e881c8697e5fd903a20fe6be3a85b64899022f5cc31a6d0f0aae190d48573d3f
eb1bcdaaca0914840e4317aa737288a8dc7141b9095e2103e6d76c0108c93518
f36cde3f905e1ab28f54f35b289491c0df6e4c6614d4a225036682e0fac1a3e4
f3d7c76ecd236587441b96d55db019057e7d74ca6b48b96f08600a9b56fbdfb9
fe9eeda65b896e9b83542df4052927a5f63070e353542ce9a7d223df36c3f6b7