
www.bankrotrf-help.ru
159.194.202.206
Public Scan
Open in
urlscan Pro
http://www.bankrotrf-help.ru/ 3mo old
Effective URL:
https://www.bankrotrf-help.ru/ 3mo old
Submission: On September 05 via api (September 5th 2026, 3:35:20 pm UTC) from US — Scanned from DE
Summary
TLS certificate: Issued by YE2 on August 19th 2026. Valid for: 3mo.
This is the only time www.bankrotrf-help.ru was scanned on urlscan.io!
urlscan.io Verdict: No classification
Domain & IP information
| IP Address | AS Autonomous System | ||
|---|---|---|---|
| 29 | 159.194.202.206 159.194.202.206 | 198610 (BEGET-AS ...) (BEGET-AS Beget LLC) | |
| 4 | 90.156.233.120 90.156.233.120 | 47764 (VK-AS LLC VK) (VK-AS LLC VK) | |
| 4 | 2a13:1ec0::1037 2a13:1ec0::1037 | 201589 (EdgeAmLLC...) (EdgeAmLLC "EDGEAM" LLC) | |
| 3 | 90.156.232.15 90.156.232.15 | 47764 (VK-AS LLC VK) (VK-AS LLC VK) | |
| 2 | 2a00:b4c0:910... 2a00:b4c0:9100:b000::d | 47764 (VK-AS LLC VK) (VK-AS LLC VK) | |
| 42 | 5 |
ASN198610 (BEGET-AS Beget LLC, RU)
| www.bankrotrf-help.ru 3mo old |
ASN201589 (EdgeAmLLC "EDGEAM" LLC, AM)
| static.tildacdn.com 10yr old |
ASN47764 (VK-AS LLC VK, RU)
| privacy-cs.mail.ru 3yr old |
| Apex Domain Subdomains |
Transfer | |
|---|---|---|
| 29 |
bankrotrf-help.ru
www.bankrotrf-help.ru 3mo old |
1 MB |
| 9 |
mail.ru
top-fwz1.mail.ru — Cisco Umbrella Rank: 14592 10yr old privacy-cs.mail.ru — Cisco Umbrella Rank: 17537 3yr old |
47 KB |
| 4 |
tildacdn.com
static.tildacdn.com — Cisco Umbrella Rank: 75270 10yr old |
3 KB |
| 42 | 3 |
| Domain | Requested by | |
|---|---|---|
| 29 | www.bankrotrf-help.ru |
www.bankrotrf-help.ru
|
| 5 | privacy-cs.mail.ru |
top-fwz1.mail.ru
privacy-cs.mail.ru |
| 4 | static.tildacdn.com |
www.bankrotrf-help.ru
|
| 4 | top-fwz1.mail.ru |
www.bankrotrf-help.ru
top-fwz1.mail.ru |
| 42 | 4 |
This site contains no links.
| Subject Issuer | Validity | Valid | |
|---|---|---|---|
| bankrotrf-help.ru YE2 |
2026-08-19 - 2026-11-17 |
3mo | crt.sh |
| *.mail.ru HARICA DV TLS RSA |
2025-09-19 - 2026-09-19 |
1yr | crt.sh |
| *.tildacdn.com GlobeSSL DV CA |
2026-02-03 - 2027-02-20 |
1yr | crt.sh |
This page contains 1 frames:
Primary Page:
https://www.bankrotrf-help.ru/
Frame ID: 9E1B3E5CF505856C854265163AD878D2
Requests: 40 HTTP requests in this frame
Screenshot
Page Title
Региональный центр списания долговPage URL History Show full URLs
-
http://www.bankrotrf-help.ru/
HTTP 307
https://www.bankrotrf-help.ru/ Page URL
Detected technologies
 Tilda
(CMS)
Expand
Detected patterns
- tilda(?:cdn|\.ws|-blocks)
 Vue.js
(JavaScript frameworks)
Expand
Detected patterns
- <(?!svg)[^>]+\sdata-v(?:ue)?-
 Font Awesome
(Font scripts)
Expand
Detected patterns
- (?:F|f)o(?:n|r)t-?(?:A|a)wesome(?:.*?([0-9a-fA-F]{7,40}|[\d]+(?:.[\d]+(?:.[\d]+)?)?)|)
Page Statistics
0 Outgoing links
These are links going to different origins than the main page.
Page URL History
This captures the URL locations of the websites, including HTTP redirects and client-side redirects via JavaScript or Meta fields.
-
http://www.bankrotrf-help.ru/
HTTP 307
https://www.bankrotrf-help.ru/ Page URL
Redirected requests
There were HTTP redirect chains for the following requests:
42 HTTP transactions
0 data transactions
| Method Protocol |
Status | Resource Path |
Size x-fer |
Time Latency |
Type MIME-Type |
IP Location |
|||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
|
GET H/1.1 |
200 OK |
Primary Request
/
Show response
www.bankrotrf-help.ru/ Redirect Chain
|
2 KB 2 KB |
300ms
95ms |
Document
text/html |
159.194.202.206 BEGET-AS Beget LLC |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
all.min.css
www.bankrotrf-help.ru/vendor/fontawesome/css/ |
100 KB 100 KB |
105ms
104ms |
Stylesheet
text/css |
159.194.202.206 BEGET-AS Beget LLC |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
app-DU-UbqV3.css
www.bankrotrf-help.ru/build/assets/ |
30 KB 31 KB |
240ms
119ms |
Stylesheet
text/css |
159.194.202.206 BEGET-AS Beget LLC |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
app-zvv4YJpV.js
Show response
www.bankrotrf-help.ru/build/assets/ |
163 KB 164 KB |
237ms
116ms |
Script
application/javascript |
159.194.202.206 BEGET-AS Beget LLC |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
code.js
Show response
top-fwz1.mail.ru/js/ |
48 KB 20 KB |
182ms
58ms |
Script
application/javascript |
90.156.233.120 VK-AS LLC VK |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
logo-new.webp
www.bankrotrf-help.ru/assets/ |
55 KB 55 KB |
68ms
66ms |
Image
image/webp |
159.194.202.206 BEGET-AS Beget LLC |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
woman.webp
www.bankrotrf-help.ru/assets/ |
214 KB 214 KB |
139ms
137ms |
Image
image/webp |
159.194.202.206 BEGET-AS Beget LLC |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
femida.webp
www.bankrotrf-help.ru/assets/ |
103 KB 103 KB |
84ms
82ms |
Image
image/webp |
159.194.202.206 BEGET-AS Beget LLC |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
wallet.svg
static.tildacdn.com/tild3237-6165-4263-a332-333866343434/ |
615 B 534 B |
93ms
15ms |
Image
image/svg+xml |
2a13:1ec0::1037 EdgeAmLLC "EDGEAM... |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
doc.svg
static.tildacdn.com/tild6163-6665-4231-b766-386231323537/ |
1 KB 762 B |
91ms
14ms |
Image
image/svg+xml |
2a13:1ec0::1037 EdgeAmLLC "EDGEAM... |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
like.svg
static.tildacdn.com/tild3964-3337-4166-a162-383032636130/ |
1 KB 738 B |
95ms
17ms |
Image
image/svg+xml |
2a13:1ec0::1037 EdgeAmLLC "EDGEAM... |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
lock.svg
static.tildacdn.com/tild3233-3137-4262-a234-363833383034/ |
1 KB 807 B |
94ms
17ms |
Image
image/svg+xml |
2a13:1ec0::1037 EdgeAmLLC "EDGEAM... |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
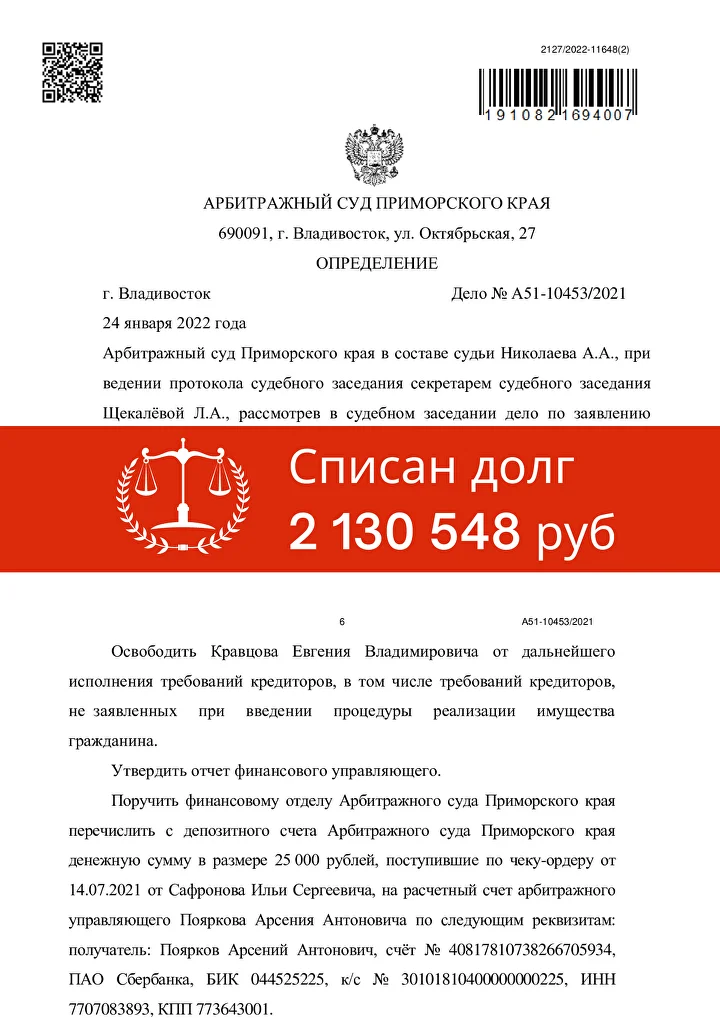
act1.webp
www.bankrotrf-help.ru/assets/ |
84 KB 84 KB |
238ms
116ms |
Image
image/webp |
159.194.202.206 BEGET-AS Beget LLC |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
act2.webp
www.bankrotrf-help.ru/assets/ |
99 KB 100 KB |
241ms
117ms |
Image
image/webp |
159.194.202.206 BEGET-AS Beget LLC |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
act3.webp
www.bankrotrf-help.ru/assets/ |
88 KB 89 KB |
146ms
82ms |
Image
image/webp |
159.194.202.206 BEGET-AS Beget LLC |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
prev1.webp
www.bankrotrf-help.ru/assets/ |
21 KB 22 KB |
130ms
100ms |
Image
image/webp |
159.194.202.206 BEGET-AS Beget LLC |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
logo.webp
www.bankrotrf-help.ru/assets/ |
16 KB 16 KB |
62ms
61ms |
Image
image/webp |
159.194.202.206 BEGET-AS Beget LLC |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
prev3.webp
www.bankrotrf-help.ru/assets/ |
17 KB 17 KB |
82ms
82ms |
Image
image/webp |
159.194.202.206 BEGET-AS Beget LLC |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
prev4.webp
www.bankrotrf-help.ru/assets/ |
29 KB 29 KB |
61ms
61ms |
Image
image/webp |
159.194.202.206 BEGET-AS Beget LLC |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
prev5.webp
www.bankrotrf-help.ru/assets/ |
18 KB 18 KB |
93ms
93ms |
Image
image/webp |
159.194.202.206 BEGET-AS Beget LLC |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
prev6.webp
www.bankrotrf-help.ru/assets/ |
25 KB 25 KB |
64ms
63ms |
Image
image/webp |
159.194.202.206 BEGET-AS Beget LLC |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
prev7.webp
www.bankrotrf-help.ru/assets/ |
20 KB 21 KB |
81ms
80ms |
Image
image/webp |
159.194.202.206 BEGET-AS Beget LLC |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
prev8.webp
www.bankrotrf-help.ru/assets/ |
19 KB 20 KB |
67ms
67ms |
Image
image/webp |
159.194.202.206 BEGET-AS Beget LLC |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
prev9.jpg
www.bankrotrf-help.ru/assets/ |
26 KB 26 KB |
61ms
61ms |
Image
image/jpeg |
159.194.202.206 BEGET-AS Beget LLC |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
prev10.webp
www.bankrotrf-help.ru/assets/ |
18 KB 18 KB |
66ms
66ms |
Image
image/webp |
159.194.202.206 BEGET-AS Beget LLC |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
prev11.jpg
www.bankrotrf-help.ru/assets/ |
26 KB 26 KB |
64ms
64ms |
Image
image/jpeg |
159.194.202.206 BEGET-AS Beget LLC |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
prev12.jpg
www.bankrotrf-help.ru/assets/ |
24 KB 24 KB |
67ms
66ms |
Image
image/jpeg |
159.194.202.206 BEGET-AS Beget LLC |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
prev13.jpg
www.bankrotrf-help.ru/assets/ |
26 KB 26 KB |
92ms
91ms |
Image
image/jpeg |
159.194.202.206 BEGET-AS Beget LLC |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
prev14.jpg
www.bankrotrf-help.ru/assets/ |
25 KB 26 KB |
67ms
67ms |
Image
image/jpeg |
159.194.202.206 BEGET-AS Beget LLC |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
prev15.webp
www.bankrotrf-help.ru/assets/ |
19 KB 19 KB |
78ms
78ms |
Image
image/webp |
159.194.202.206 BEGET-AS Beget LLC |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
prev17.jpg
www.bankrotrf-help.ru/assets/ |
25 KB 26 KB |
72ms
71ms |
Image
image/jpeg |
159.194.202.206 BEGET-AS Beget LLC |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
femida-timer.webp
www.bankrotrf-help.ru/assets/ |
67 KB 67 KB |
64ms
64ms |
Image
image/webp |
159.194.202.206 BEGET-AS Beget LLC |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
fa-solid-900.woff2
www.bankrotrf-help.ru/vendor/fontawesome/webfonts/ |
153 KB 153 KB |
179ms
126ms |
Font
font/woff2 |
159.194.202.206 BEGET-AS Beget LLC |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
sync-loader.js
Show response
privacy-cs.mail.ru/static/ |
83 KB 22 KB |
1857ms
76ms |
Script
application/javascript |
90.156.232.15 VK-AS LLC VK |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
dyn-goal-config.js
Show response
top-fwz1.mail.ru/js/ |
3 KB 2 KB |
60ms
56ms |
Script
application/javascript |
90.156.233.120 VK-AS LLC VK |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
counter
top-fwz1.mail.ru/ |
43 B 1 KB |
57ms
54ms |
Image
image/gif |
90.156.233.120 VK-AS LLC VK |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
tracker
top-fwz1.mail.ru/ |
43 B 1 KB |
59ms
58ms |
Image
image/gif |
90.156.233.120 VK-AS LLC VK |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
favicon.png
www.bankrotrf-help.ru/assets/ |
10 KB 10 KB |
60ms
60ms |
Other
image/png |
159.194.202.206 BEGET-AS Beget LLC |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
OPTIONS H/1.1 |
200 OK |
/
privacy-cs.mail.ru/fp/ |
0 0 |
1176ms
48ms |
Preflight
application/octet-stream |
2a00:b4c0:9100:b000::d VK-AS LLC VK |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H/1.1 |
200 OK |
/
privacy-cs.mail.ru/fp/ |
0 0 |
78ms
78ms |
Fetch
application/octet-stream |
90.156.232.15 VK-AS LLC VK |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H/1.1 |
200 OK |
/
privacy-cs.mail.ru/fp/ |
0 0 |
78ms
76ms |
Fetch
application/octet-stream |
90.156.232.15 VK-AS LLC VK |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
OPTIONS H/1.1 |
200 OK |
/
privacy-cs.mail.ru/fp/ |
0 0 |
193ms
49ms |
Preflight
application/octet-stream |
2a00:b4c0:9100:b000::d VK-AS LLC VK |
|||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||










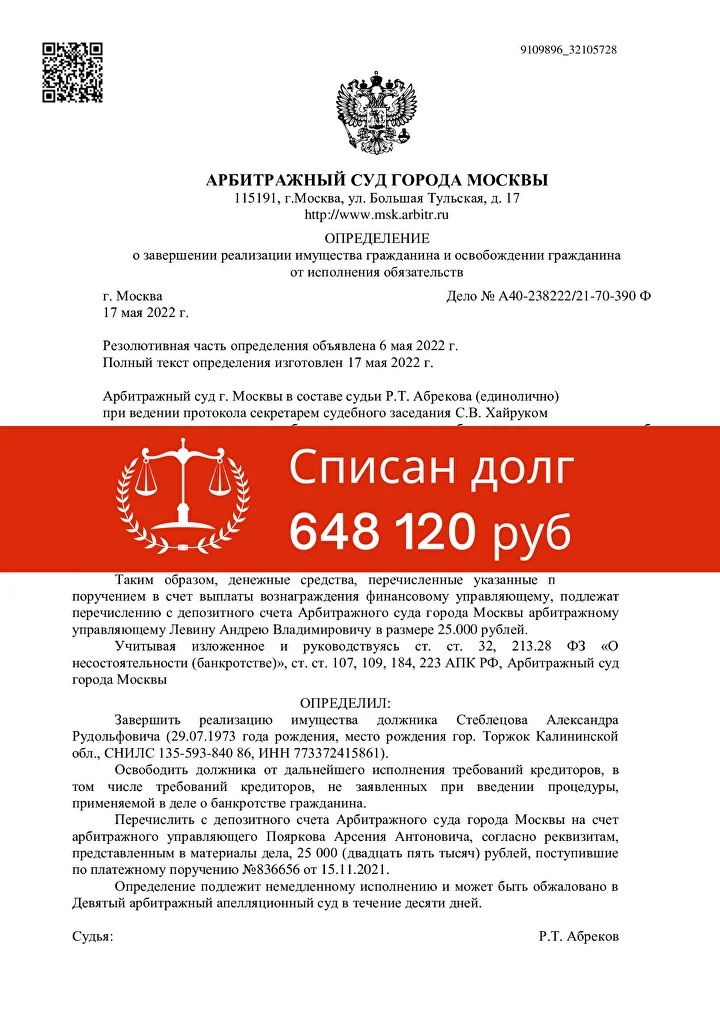


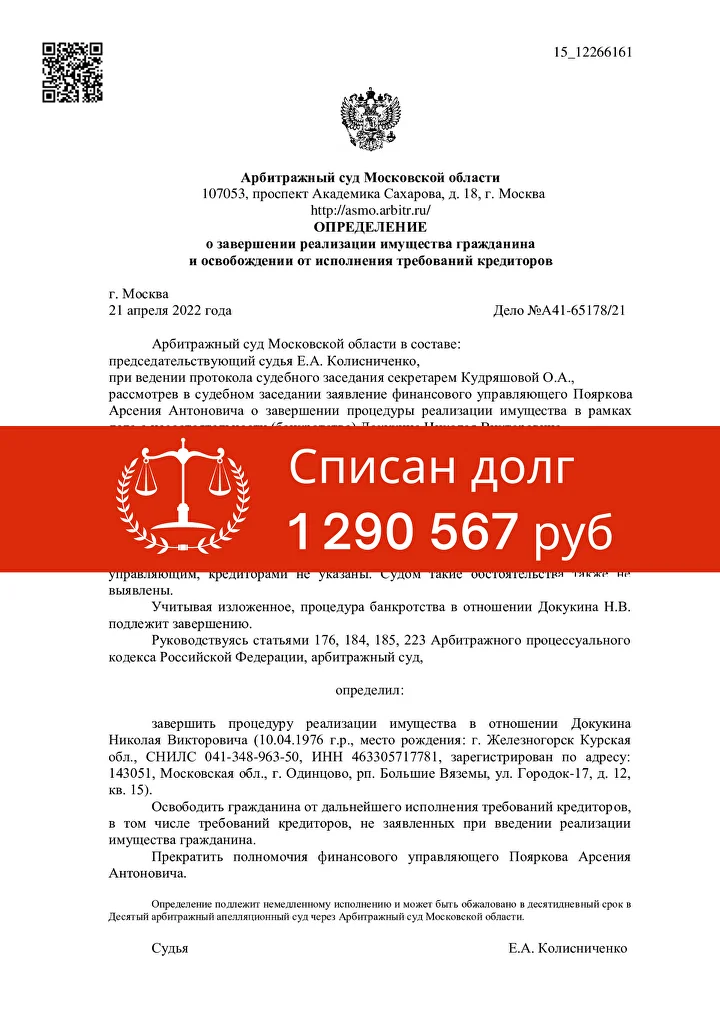




































Verdicts & Comments Add Verdict or Comment
8 JavaScript Window variables
These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.
object| 0 object| __APP__ object| _tmr object| __VUE_INSTANCE_SETTERS__ object| __VUE_SSR_SETTERS__ boolean| __VUE__ number| rb_sync_refresh_time object| rb_sync8 Cookies
Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.
| Domain/Path | Expires | Name / Value | |||
|---|---|---|---|---|---|
| www.bankrotrf-help.ru/ | 1970-01-21 16:50:29 |
Name: XSRF-TOKEN Value: eyJpdiI6ImtWajkrQ2ZGQ2p0ZFFVdmIvMUNsM1E9PSIsInZhbHVlIjoiaDFKZHN2MVFhTHpsQm04ME5Ja1VKWHhoTmZXbkZsNnN0c0xkZy9yKzczVVIxSit4dmVLSWxQN2l5N0VKQUROd3kwNWZKcTJDTGhNMmVhTXlWTnF5c1FwZTlzR253Tkh5OUxzY3NBR2FKZmhIUm1nRi94NkNHWnhDdHVubmh1QmwiLCJtYWMiOiI1MmZmNzJmN2VkNTNjMTE1MDFjZjA3ZjM5NzU4NjNjNjQ4ZmRhM2RhYzEzMTc1Mzg1Y2M0MTQzNTVlYzNiYjBjIiwidGFnIjoiIn0%3D |
|||
| www.bankrotrf-help.ru/ | 1970-01-21 16:50:29 |
Name: bankrotrf-help-session Value: eyJpdiI6ImVNVzBTdEMvOHVROFR1UEJWbFFRRXc9PSIsInZhbHVlIjoiMUJhNjlXdGhLRmVoODZLSmMrbklWejRmVU9UYmI5S0pEMkh1VTRXeEk4Q3JpSVBDWGJlYnFMUFREQ0pLSVZremM3cUR2YVpqUndGVlJqMDFtWE1QL2FTMHNEYWxqVE9STU01VXl5VE42L3hCVkkvTnhSb2N2azVBeTdTWjRZckwiLCJtYWMiOiJjZWU1OTczMDUzOWY2MjFmNmM1ZGZlYmNiZGY1OWViYTczMTljOTdhOWIzMzZiMDAxNjU4MzJiODNhMmUzNGZiIiwidGFnIjoiIn0%3D |
|||
| .bankrotrf-help.ru/ | 1970-01-22 00:49:53 |
Name: tmr_lvid Value: d2f62422b6b92d6b262f3d3295078bb4 |
|||
| .bankrotrf-help.ru/ | 1970-01-22 00:49:53 |
Name: tmr_lvidTS Value: 1788622521023 |
|||
| www.bankrotrf-help.ru/ | 1970-01-21 17:00:27 |
Name: domain_sid Value: h66r91rg6sVbX-_k6GWmW%3A1788622522966 |
|||
| top-fwz1.mail.ru/ | 1970-01-22 01:37:24 |
Name: PVID Value: 0m3z0b17Gm2g00003v3pzS2g:::0-0-0-fb68f79-0-fb68f7a:CAASEB8kf_Hs9REK9CFkxLU_rj4aYK3_pfe28o9HcrxGbdmlTwYkgcaZ3ZWAb4uW6IaWBfseG5quTbEBASGJLTA_vq3oOVq6tSPahu7UBrXDdvsBRAIiqSZf34MNpWXKbbCaEwAXt5VmL2Rty699sEzCDiY4Ww |
|||
| .mail.ru/ | 1970-01-22 01:37:24 |
Name: VID Value: 0m3z0b17Gm2g00003v3pzS2g:::0-0-0-fb68f79-0-fb68f7a:CAASEB8kf_Hs9REK9CFkxLU_rj4aYK3_pfe28o9HcrxGbdmlTwYkgcaZ3ZWAb4uW6IaWBfseG5quTbEBASGJLTA_vq3oOVq6tSPahu7UBrXDdvsBRAIiqSZf34MNpWXKbbCaEwAXt5VmL2Rty699sEzCDiY4Ww |
|||
| www.bankrotrf-help.ru/ | 1970-01-21 16:51:48 |
Name: tmr_detect Value: 0%7C1788622523293 |
2 Console Messages
A page may trigger messages to the console to be logged. These are often error messages about being unable to load a resource or execute a piece of JavaScript. Sometimes they also provide insight into the technology behind a website.
| Source | Level | URL Text |
|---|
Indicators
This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.
privacy-cs.mail.ru
static.tildacdn.com
top-fwz1.mail.ru
www.bankrotrf-help.ru
159.194.202.206
2a00:b4c0:9100:b000::d
2a13:1ec0::1037
90.156.232.15
90.156.233.120
013470547f611912bbba8aa96eac9731ad71862e1bbcb9f58580de761ba1c1ab
09318f8ddfe37fe2ca60aa92fea311520208408db70f1e4ece432194c7177c12
0e7e3045519beaff2095d4a64b8dfb1b581013eb5b8f4b3549983c69abe7139b
23192737ae1825ad59cfe4e9bfe5e0a3d88a5933aac82947c2cb78d4ba6abaed
24e480e4659fbae818853a38f8a3036f529f539024dc3e772c0b594ce02ea9db
27100bde4adbfdcac28b3eba0d26f5e5993eea82dbcedc21773444fa0e4d898b
27cdc11a801fb9f0eb779ab41fc4c6943c1fb3c24f2fc5a4ce8a01c1a1c55de3
29e7355bf7edfc4eaa80896ced706dfe0c1591a76fe63b21d56a190fd33357e6
474320b22308b651f376386e8ef87141e3f7b9e45c67371473a8f1bbe5fdea3e
48d8a5e05472be6f034a4d533665d3bd6c0bf92bbe59e9ef55a5aa1b530b8eea
4b92d7e6ba2eddaac4cbd31c87ab19503c25e9e6a593d85f8df22e0c1ac303da
69510c5ef95607c2cf30cd88ec53595bdb6f5b8fb3e61f21e463dc9ba9d2e420
6c1551b219ed647b1940e4c5a00a869ed63d2817bf81ec9ddcdb56c09159d79b
6eee48366993de9f9326b363ca0c6dd6af0167535f158f0ec38f6ef76fce1dc2
716c6922857160e868217cd702c7e32072ee640e3d9d30f3fb9452c80fea9ced
717f5632eac507594e29676bcdab5de9521ec216dae0ec961e661573587764a6
75c678f3f867718db9558002fe3cd872803c3539c27b5006a29ca9667ada1575
77ead775ec775283989d380c8b5aa0a6c10a5e6670fafa86c8a752b052f58347
7ee7c60698e5e146979307fbc979c5e02d82dc32b2f029147c9db3114cce071b
8790701e3eec882a3d3d9a39452c29e4093e1a6cafded9205f05fc75b02532f0
8b0aaaf1193fc5b7e9ee4b1bbdbea6ddc50564b3e144661b128d9129d6593d15
8eefa92d87bc30c690b104eaf8ed5e801239907afeb14e38772988781dc48715
914a7aa4b39e3a780292ede97e42a4f90c99e52d2bf1e0e5d35e549dffc66951
91968b7c7e14d92c265f075c51632441cac2122aa63a967b292a6112d385dfba
91edc8494dc960e41bf4c9e49b33e7faea26b317fae9b34e8033520d6f719d03
9f898f83c4ac8d8739ff8e9caf4f9b27ab20a781a209926d82afd3940c052819
ad41d12b5e8d1032897a5401fbb0945c31ed29c4bd6fe594b296d80746f0495f
c880eb3d25c765d399840aa204fec22b3230310991089f14781f09a35ed80b8a
cd326fa58bd027fa2297eacaeac5c43b0a9ee62a014ed424a8c45cd4e8be1533
ce24fe54ce3a08c6fffddbbd0efeda3cf530ea519bef2226d98139a1cb7d10d8
d0d674a3279437e26ff13d6cb4ff9bd2534143da70748c35b17dff8fe56d3c28
d161d249fab5345f43307c9a9ce19a5fc0cfad6ba5db6e8a7664479d4c9b76e8
dc1d4b2a1a33b592f1b8ccae3c07c5090d757909043fa7e02b3f9679ea141d99
dcb80feea04478703cd45529b33af1c5bab72cd0e48dc44e3a470b891f286dbd
f0c093817c2a39bd1628471967a6a52d588b569d9572557a2e270e76c9f31749
f4c5a5b297e623bc159679563a4d1eb16e409ca3b57698fbc00fd2c907dadae0
f9b041696ae5ed18aa5b45492052cd4a30d454ab80e59d6b59c4222c5fe71306