Summary

This website contacted 101 IPs in 12 countries across 76 domains to perform 667 HTTP transactions. The main IP is 18.65.39.76, located in United States and belongs to AMAZON-02 - Amazon.com, Inc., US. The main domain is abc7.com. The Cisco Umbrella rank of the primary domain is 199759. 10yr old
TLS certificate: Issued by Amazon RSA 2048 M04 on August 7th 2026. Valid for: 7mo.
This is the only time abc7.com was scanned on urlscan.io!

Domain & IP information

IP Address AS Autonomous System
1 3 18.65.39.76 18.65.39.76 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
29 13.32.121.29 13.32.121.29 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
10 3.124.173.63 3.124.173.63 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
5 13.32.121.2 13.32.121.2 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 54.192.35.118 54.192.35.118 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
11 104.18.87.42 104.18.87.42 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
1 100.60.116.23 100.60.116.23 14618 (AMAZON-AES) (AMAZON-AES - Amazon.com)
5 13.226.244.19 13.226.244.19 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 162.247.243.39 162.247.243.39 54113 (FASTLY) (FASTLY - Fastly)
4 104.17.208.240 104.17.208.240 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
4 99.84.152.107 99.84.152.107 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
3 162.247.243.29 162.247.243.29 54113 (FASTLY) (FASTLY - Fastly)
1 3.173.161.33 3.173.161.33 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 3.173.161.103 3.173.161.103 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 18.238.243.39 18.238.243.39 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
2 18.245.63.132 18.245.63.132 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
32 151.101.193.44 151.101.193.44 54113 (FASTLY) (FASTLY - Fastly)
2 104.26.3.116 104.26.3.116 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
2 3.221.141.84 3.221.141.84 14618 (AMAZON-AES) (AMAZON-AES - Amazon.com)
2 142.251.14.155 142.251.14.155 15169 (GOOGLE) (GOOGLE - Google LLC)
5 3.161.82.34 3.161.82.34 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 104.26.2.116 104.26.2.116 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
3 151.101.66.202 151.101.66.202 54113 (FASTLY) (FASTLY - Fastly)
1 2 178.250.1.12 178.250.1.12 44788 (ASN-CRITE...) (ASN-CRITEO-EUROPE Criteo Technology SAS)
3 18.239.105.88 18.239.105.88 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
4 142.250.154.154 142.250.154.154 15169 (GOOGLE) (GOOGLE - Google LLC)
1 104.16.120.9 104.16.120.9 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
2 184.24.77.190 184.24.77.190 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.)
2 6 18.244.18.27 18.244.18.27 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 52.51.56.224 52.51.56.224 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
7 15.197.135.246 15.197.135.246 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
229 3.161.82.115 3.161.82.115 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
11 185.106.33.48 185.106.33.48 200478 (TABOOLA-A...) (TABOOLA-AS Taboola.com ltd)
10 151.101.1.44 151.101.1.44 54113 (FASTLY) (FASTLY - Fastly)
4 63.140.62.210 63.140.62.210 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
5 142.251.150.119 142.251.150.119 15169 (GOOGLE) (GOOGLE - Google LLC)
1 2 4.208.245.100 4.208.245.100 8075 (MICROSOFT...) (MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation)
2 2 142.251.13.154 142.251.13.154 15169 (GOOGLE) (GOOGLE - Google LLC)
4 104.18.38.107 104.18.38.107 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
8 23 142.251.13.157 142.251.13.157 15169 (GOOGLE) (GOOGLE - Google LLC)
1 18.239.18.12 18.239.18.12 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 34.102.146.192 34.102.146.192 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC)
1 18.239.18.41 18.239.18.41 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 23.52.180.230 23.52.180.230 16625 (AKAMAI-AS) (AKAMAI-AS - Akamai Technologies)
1 104.20.23.13 104.20.23.13 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
1 2.16.241.207 2.16.241.207 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.)
1 104.17.207.5 104.17.207.5 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
1 18.66.102.31 18.66.102.31 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 172.67.205.57 172.67.205.57 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
1 34.96.70.87 34.96.70.87 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC)
1 142.251.110.132 142.251.110.132 15169 (GOOGLE) (GOOGLE - Google LLC)
2 142.251.14.95 142.251.14.95 15169 (GOOGLE) (GOOGLE - Google LLC)
2 23.56.204.67 23.56.204.67 16625 (AKAMAI-AS) (AKAMAI-AS - Akamai Technologies)
9 142.251.14.94 142.251.14.94 15169 (GOOGLE) (GOOGLE - Google LLC)
2 18.245.60.26 18.245.60.26 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 141.226.224.32 141.226.224.32 200478 (TABOOLA-A...) (TABOOLA-AS Taboola.com ltd)
6 142.251.14.132 142.251.14.132 15169 (GOOGLE) (GOOGLE - Google LLC)
1 2 35.227.252.103 35.227.252.103 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC)
2 142.250.154.94 142.250.154.94 15169 (GOOGLE) (GOOGLE - Google LLC)
5 45.87.133.75 45.87.133.75 208398 (TELETECH ...) (TELETECH Edge Technology Plus d.o.o. Beograd)
3 212.102.56.178 212.102.56.178 60068 (CDN77 Dat...) (CDN77 Datacamp Limited)
6 142.251.127.157 142.251.127.157 15169 (GOOGLE) (GOOGLE - Google LLC)
1 3.33.135.48 3.33.135.48 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 108.129.59.25 108.129.59.25 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 34.8.2.179 34.8.2.179 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC)
5 141.226.228.48 141.226.228.48 200478 (TABOOLA-A...) (TABOOLA-AS Taboola.com ltd)
1 192.145.111.2 192.145.111.2 207522 (mygaru_au...) (mygaru_au Mygaru OU Private Limited Company)
1 23.50.131.159 23.50.131.159 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.)
1 135.125.170.108 135.125.170.108 16276 (OVH OVH SAS) (OVH OVH SAS)
5 3.233.158.26 3.233.158.26 14618 (AMAZON-AES) (AMAZON-AES - Amazon.com)
5 35.244.159.8 35.244.159.8 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC)
1 87.248.119.251 87.248.119.251 203220 (YAHOO-DEB...) (YAHOO-DEB Yahoo-UK Limited)
8 8 35.71.131.137 35.71.131.137 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
5 5 185.184.8.90 185.184.8.90 204995 (RTB-HOUSE...) (RTB-HOUSE-AMS RTB Marketing and Tech Services Ltd)
3 3 37.157.5.86 37.157.5.86 198622 (ADFORM Ad...) (ADFORM Adform A/S)
1 195.181.170.18 195.181.170.18 60068 (CDN77 Dat...) (CDN77 Datacamp Limited)
1 79.127.216.203 79.127.216.203 60068 (CDN77 Dat...) (CDN77 Datacamp Limited)
3 130.211.115.4 130.211.115.4 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC)
4 23.219.139.145 23.219.139.145 16625 (AKAMAI-AS) (AKAMAI-AS - Akamai Technologies)
3 17 104.18.27.193 104.18.27.193 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
2 108.138.7.109 108.138.7.109 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
3 13.32.121.65 13.32.121.65 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 44.193.192.39 44.193.192.39 14618 (AMAZON-AES) (AMAZON-AES - Amazon.com)
11 142.251.127.155 142.251.127.155 15169 (GOOGLE) (GOOGLE - Google LLC)
4 23.36.162.16 23.36.162.16 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.)
4 63.140.62.236 63.140.62.236 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
4 69.173.144.137 69.173.144.137 26667 (RUBICONPR...) (RUBICONPROJECT - Magnite)
4 6 69.173.144.165 69.173.144.165 26667 (RUBICONPR...) (RUBICONPROJECT - Magnite)
1 1 34.36.133.20 34.36.133.20 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC)
1 1 47.253.61.56 47.253.61.56 45102 (ALIBABA-C...) (ALIBABA-CN-NET - Alibaba (US) Technology Co.)
1 1 35.186.193.173 35.186.193.173 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC)
1 13.32.121.49 13.32.121.49 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
8 199.127.194.128 199.127.194.128 11483 (CONVIVA-AS) (CONVIVA-AS - Conviva)
16 2.19.126.208 2.19.126.208 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.)
1 23.207.210.93 23.207.210.93 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.)
2 2 216.19.192.2 216.19.192.2 26667 (RUBICONPR...) (RUBICONPROJECT - Magnite)
5 9 69.173.144.138 69.173.144.138 26667 (RUBICONPR...) (RUBICONPROJECT - Magnite)
1 3 18.239.36.83 18.239.36.83 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 2 108.138.26.109 108.138.26.109 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 104.18.41.41 104.18.41.41 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
3 3 18.200.209.28 18.200.209.28 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 163.5.194.53 163.5.194.53 60558 (SECUREDSE...) (SECUREDSERVERS-EU PHOENIX NAP)
1 1 35.173.83.176 35.173.83.176 14618 (AMAZON-AES) (AMAZON-AES - Amazon.com)
1 4.208.244.57 4.208.244.57 8075 (MICROSOFT...) (MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation)
1 104.18.41.104 104.18.41.104 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
2 3 34.111.113.62 34.111.113.62 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC)
7 8 103.231.98.106 103.231.98.106 62713 (AS-PUBMATIC) (AS-PUBMATIC - PubMatic)
4 4 198.47.127.205 198.47.127.205 62713 (AS-PUBMATIC) (AS-PUBMATIC - PubMatic)
1 1 198.47.127.20 198.47.127.20 62713 (AS-PUBMATIC) (AS-PUBMATIC - PubMatic)
1 18.239.83.90 18.239.83.90 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 162.159.141.246 162.159.141.246 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
1 1 35.208.249.213 35.208.249.213 43515 (YOUTUBE G...) (YOUTUBE Google Ireland Limited)
3 3 35.214.136.108 35.214.136.108 15169 (GOOGLE) (GOOGLE - Google LLC)
1 1 193.0.160.131 193.0.160.131 54312 (ROCKETFUEL) (ROCKETFUEL - Rocket Fuel Inc.)
1 2 151.101.2.49 151.101.2.49 54113 (FASTLY) (FASTLY - Fastly)
1 1 52.214.155.69 52.214.155.69 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
2 2 34.36.216.150 34.36.216.150 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC)
667 101
Apex Domain
Subdomains
Transfer
234 disney.com
login.disney.com — Cisco Umbrella Rank: 15619 2yr old
2 MB
59 taboola.com
cdn.taboola.com — Cisco Umbrella Rank: 1119 10yr old
trc.taboola.com — Cisco Umbrella Rank: 753 10yr old
il-trc-events.taboola.com — Cisco Umbrella Rank: 18805 5yr old
images.taboola.com — Cisco Umbrella Rank: 1775 10yr old
vidstat.taboola.com — Cisco Umbrella Rank: 3899 9yr old
cds.taboola.com — Cisco Umbrella Rank: 1833 8yr old
am-match.taboola.com — Cisco Umbrella Rank: 17779 7yr old
imprammp.taboola.com — Cisco Umbrella Rank: 17257 10yr old
wf.taboola.com — Cisco Umbrella Rank: 5243 9yr old
am-vid-events.taboola.com — Cisco Umbrella Rank: 17689 6yr old
sync.taboola.com — Cisco Umbrella Rank: 1314 7yr old
2 MB
29 abcotvs.net
assets-cdn.abcotvs.net — Cisco Umbrella Rank: 49426 7yr old
cdn.abcotvs.net Failed 8yr old
2 MB
25 rubiconproject.com 11 redirects
eus.rubiconproject.com — Cisco Umbrella Rank: 814 9yr old
prebid-server.rubiconproject.com — Cisco Umbrella Rank: 1282 9yr old
token.rubiconproject.com — Cisco Umbrella Rank: 734 10yr old
pixel-us-east.rubiconproject.com — Cisco Umbrella Rank: 2008 9yr old
pixel.rubiconproject.com — Cisco Umbrella Rank: 573 10yr old
33 KB
21 googlesyndication.com
0c94aa5156cf0935a827c3b9863ae691.safeframe.googlesyndication.com 1mo old
tpc.googlesyndication.com — Cisco Umbrella Rank: 236 14yr old
pagead2.googlesyndication.com — Cisco Umbrella Rank: 117 10yr old
116 KB
19 doubleclick.net 10 redirects
securepubads.g.doubleclick.net — Cisco Umbrella Rank: 345 10yr old
cm.g.doubleclick.net — Cisco Umbrella Rank: 337 10yr old
243 KB
17 dssott.com
cmp-abcotv.media.dssott.com — Cisco Umbrella Rank: 125711 1yr old
linear-abcotv-ftc-na-east-1.media.dssott.com Failed 1yr old
linear-abcotv-akc-na-east-1.media.dssott.com — Cisco Umbrella Rank: 204019 1yr old
2 MB
17 casalemedia.com 3 redirects
ssum.casalemedia.com — Cisco Umbrella Rank: 2342 10yr old
dsum-sec.casalemedia.com — Cisco Umbrella Rank: 841 12yr old
ssum-sec.casalemedia.com — Cisco Umbrella Rank: 827 12yr old
dsum.casalemedia.com — Cisco Umbrella Rank: 1829 10yr old
11 KB
15 bamgrid.com
pcs.bamgrid.com — Cisco Umbrella Rank: 7516 4yr old
hiveplayer-static.bamgrid.com — Cisco Umbrella Rank: 12317 2yr old
client-sdk-configs.bamgrid.com — Cisco Umbrella Rank: 5052 1yr old
disney-entertainment.api.edge.bamgrid.com — Cisco Umbrella Rank: 36032 1yr old
disney-entertainment.playback.edge.bamgrid.com — Cisco Umbrella Rank: 64927 1yr old
static-assets.bamgrid.com Failed 5yr old
playback-certs.bamgrid.com Failed 7yr old
672 KB
14 pubmatic.com 12 redirects
ads.pubmatic.com — Cisco Umbrella Rank: 691 10yr old
image8.pubmatic.com — Cisco Umbrella Rank: 940 8yr old
image2.pubmatic.com — Cisco Umbrella Rank: 982 10yr old
image4.pubmatic.com — Cisco Umbrella Rank: 1594 10yr old
simage2.pubmatic.com — Cisco Umbrella Rank: 1154 10yr old
9 KB
14 go.com
prod.gatekeeper.us-abc.symphony.edgedatg.go.com Failed 9yr old
log.go.com — Cisco Umbrella Rank: 7522 12yr old
sw88.go.com — Cisco Umbrella Rank: 26552 14yr old
cdn.registerdisney.go.com — Cisco Umbrella Rank: 6837 13yr old
26 KB
13 gstatic.com
fonts.gstatic.com — Cisco Umbrella Rank: 31 10yr old
www.gstatic.com — Cisco Umbrella Rank: 8 10yr old
729 KB
13 espn.com
dcf.espn.com — Cisco Umbrella Rank: 7537 6yr old
cdn.espn.com Failed 10yr old
pinpoint.espn.com — Cisco Umbrella Rank: 9390 5yr old
secure.espn.com — Cisco Umbrella Rank: 9625 10yr old
watch.auth.api.espn.com — Cisco Umbrella Rank: 19780 11yr old
351 KB
11 cookielaw.org
cdn.cookielaw.org — Cisco Umbrella Rank: 440 10yr old
249 KB
8 googleadservices.com
www.googleadservices.com — Cisco Umbrella Rank: 105 14yr old
62 KB
8 adsrvr.org 8 redirects
match.adsrvr.org — Cisco Umbrella Rank: 472 10yr old
5 KB
8 conviva.com
27f19c7c68e3eadf7756fb7efdb661dd8909acf9.ipv4.cws.conviva.com Failed 4yr old
27f19c7c68e3eadf7756fb7efdb661dd8909acf9.ipv6.cws.conviva.com Failed 4yr old
27f19c7c68e3eadf7756fb7efdb661dd8909acf9.cws.conviva.com — Cisco Umbrella Rank: 48976 4yr old
2 KB
7 openx.net 1 redirects
rtb.openx.net — Cisco Umbrella Rank: 776 9yr old
google-bidout-d.openx.net — Cisco Umbrella Rank: 2176 7yr old
us-u.openx.net — Cisco Umbrella Rank: 731 10yr old
eu-u.openx.net — Cisco Umbrella Rank: 1862 10yr old
2 KB
6 creativecdn.com 5 redirects
invstatic101.creativecdn.com — Cisco Umbrella Rank: 1922 4yr old
creativecdn.com — Cisco Umbrella Rank: 646 13yr old
5 KB
6 scorecardresearch.com 2 redirects
sb.scorecardresearch.com — Cisco Umbrella Rank: 238 10yr old
census-web.scorecardresearch.com — Cisco Umbrella Rank: 9032 6yr old
9 KB
5 amazon-adsystem.com 2 redirects
s.amazon-adsystem.com — Cisco Umbrella Rank: 554 14yr old
aax-eu.amazon-adsystem.com — Cisco Umbrella Rank: 1257 14yr old
3 KB
5 imrworldwide.com
cdn-gl.imrworldwide.com — Cisco Umbrella Rank: 4550 10yr old
secure-dcr.imrworldwide.com Failed 10yr old
ofobcf0jnrxzvhgar1o4dqljwayhw1788722132.nuid.imrworldwide.com Failed
8r4gmjpf7oh1f4k6kvliwheufdaa51788722132.nuid.imrworldwide.com Failed
tskekwqpdovdxtqtskdeycqal9hwq1788722137.nuid.imrworldwide.com 1mo old
86 KB
5 browser-intake-datadoghq.com
browser-intake-datadoghq.com — Cisco Umbrella Rank: 721 6yr old
2 KB
5 yango.tech
display.asas.yango.tech — Cisco Umbrella Rank: 131656 2yr old
avatars.asas.yango.tech — Cisco Umbrella Rank: 119786 2yr old
favicon.asas.yango.tech — Cisco Umbrella Rank: 286341 2yr old
205 KB
5 yango.com
eu.asas.yango.com — Cisco Umbrella Rank: 48358 2yr old
589 B
5 ad-score.com
js.ad-score.com — Cisco Umbrella Rank: 2685 11yr old
data.ad-score.com — Cisco Umbrella Rank: 2455 12yr old
189 KB
5 adtrafficquality.google
ep1.adtrafficquality.google — Cisco Umbrella Rank: 151 2yr old
ep2.adtrafficquality.google — Cisco Umbrella Rank: 166 2yr old
27 KB
5 chartbeat.com
static.chartbeat.com — Cisco Umbrella Rank: 2361 10yr old
mab.chartbeat.com — Cisco Umbrella Rank: 4026 10yr old
28 KB
5 abcotvs.com
cdn.abcotvs.com Failed — Cisco Umbrella Rank: 56749 10yr old
api.abcotvs.com — Cisco Umbrella Rank: 79777 10yr old
343 KB
5 abcnews.com
s.abcnews.com — Cisco Umbrella Rank: 35066 11yr old
258 KB
4 omtrdc.net
abcotv.hb-api.omtrdc.net — Cisco Umbrella Rank: 104233 5yr old
454 B
4 braze.com
sdk.iad-05.braze.com — Cisco Umbrella Rank: 3518 5yr old
1 KB
4 qualtrics.com
zn5hsliyrlhlj7ndr-abcotv.siteintercept.qualtrics.com — Cisco Umbrella Rank: 90519 9yr old
siteintercept.qualtrics.com — Cisco Umbrella Rank: 948 13yr old
62 KB
3 bidswitch.net 3 redirects
x.bidswitch.net — Cisco Umbrella Rank: 564 14yr old
1 KB
3 tapad.com 2 redirects
pixel.tapad.com — Cisco Umbrella Rank: 707 10yr old
1 KB
3 bidr.io 3 redirects
match.prod.bidr.io — Cisco Umbrella Rank: 849 10yr old
994 B
3 adform.net 3 redirects
c1.adform.net — Cisco Umbrella Rank: 903 13yr old
2 KB
3 adnxs.com 1 redirects
ib.adnxs.com — Cisco Umbrella Rank: 362 10yr old
3 KB
3 google.com
www.google.com — Cisco Umbrella Rank: 3 14yr old
29 KB
3 tru.am
tru.am — Cisco Umbrella Rank: 8791 13yr old
beacon.tru.am — Cisco Umbrella Rank: 11329 9yr old
12 KB
3 nr-data.net
bam.nr-data.net — Cisco Umbrella Rank: 405 10yr old
1 KB
3 abc7.com 1 redirects
abc7.com — Cisco Umbrella Rank: 199759 10yr old
72 KB
2 sitescout.com 2 redirects
pixel-sync.sitescout.com — Cisco Umbrella Rank: 931 8yr old
902 B
2 everesttech.net 1 redirects
sync-tm.everesttech.net — Cisco Umbrella Rank: 959 9yr old
689 B
2 googleapis.com
fonts.googleapis.com — Cisco Umbrella Rank: 46 10yr old
616 B
2 yahoo.com
connectid.analytics.yahoo.com — Cisco Umbrella Rank: 2130 4yr old
ups.analytics.yahoo.com — Cisco Umbrella Rank: 603 7yr old
9 KB
2 im-apps.net
dmp.im-apps.net — Cisco Umbrella Rank: 3085 10yr old
sync6.im-apps.net — Cisco Umbrella Rank: 3272 5yr old
3 KB
2 id5-sync.com
cdn.id5-sync.com — Cisco Umbrella Rank: 916 7yr old
id5-sync.com — Cisco Umbrella Rank: 596 9yr old
35 KB
2 crwdcntrl.net
tags.crwdcntrl.net — Cisco Umbrella Rank: 1103 14yr old
bcp.crwdcntrl.net — Cisco Umbrella Rank: 1401 10yr old
14 KB
2 criteo.com 1 redirects
gum.criteo.com — Cisco Umbrella Rank: 542 10yr old
1 KB
2 googletagservices.com
www.googletagservices.com — Cisco Umbrella Rank: 447 10yr old
128 KB
2 chartbeat.net
ping.chartbeat.net — Cisco Umbrella Rank: 2150 10yr old
401 B
1 adroll.com 1 redirects
d.adroll.com — Cisco Umbrella Rank: 1389 10yr old
983 B
1 rfihub.com 1 redirects
p.rfihub.com — Cisco Umbrella Rank: 1052 10yr old
778 B
1 mediago.io 1 redirects
trace.mediago.io — Cisco Umbrella Rank: 1895 6yr old
288 B
1 temu.com
www.temu.com — Cisco Umbrella Rank: 918 5yr old
632 B
1 connatix.com
capi.connatix.com — Cisco Umbrella Rank: 1260 7yr old
316 B
1 ipredictive.com 1 redirects
sync.ipredictive.com — Cisco Umbrella Rank: 1051 9yr old
516 B
1 a-mo.net
sync.a-mo.net — Cisco Umbrella Rank: 1447 3yr old
671 B
1 linkedin.com
px.ads.linkedin.com — Cisco Umbrella Rank: 373 9yr old
760 B
1 ctnsnet.com 1 redirects
cm.ctnsnet.com — Cisco Umbrella Rank: 4325 9yr old
406 B
1 ymmobi.com 1 redirects
gw-iad-bid.ymmobi.com — Cisco Umbrella Rank: 1980 3yr old
421 B
1 company-target.com 1 redirects
s.company-target.com — Cisco Umbrella Rank: 1342 5yr old
621 B
1 mygaru.com
ident.mygaru.com — Cisco Umbrella Rank: 4090 3yr old
529 B
1 spadsync.com
spadsync.com — Cisco Umbrella Rank: 6615 7yr old
75 B
1 mgaru.dev
cdn.mgaru.dev — Cisco Umbrella Rank: 4007 2yr old
2 KB
1 jsdelivr.net
cdn.jsdelivr.net — Cisco Umbrella Rank: 284 14yr old
969 B
1 fusion-platform.com
cdn.fusion-platform.com — Cisco Umbrella Rank: 9867 1yr old
2 KB
1 openxcdn.net
oa.openxcdn.net — Cisco Umbrella Rank: 2014 7yr old
10 KB
1 espncdn.com
secure.espncdn.com — Cisco Umbrella Rank: 8286 10yr old
73 KB
1 demdex.net
disney.demdex.net — Cisco Umbrella Rank: 11321 7yr old
650 B
1 appboycdn.com
js.appboycdn.com — Cisco Umbrella Rank: 4074 11yr old
63 KB
1 disneyaccount.com
cdn.disneyaccount.com — Cisco Umbrella Rank: 41786 1yr old
54 KB
1 newrelic.com
js-agent.newrelic.com — Cisco Umbrella Rank: 905 12yr old
17 KB
1 webcontentassessor.com
scripts.webcontentassessor.com — Cisco Umbrella Rank: 4189 8yr old
122 KB
0 rlcdn.com Failed
id.rlcdn.com Failed 9yr old
667 76
Domain Requested by
234 login.disney.com abc7.com
login.disney.com
29 assets-cdn.abcotvs.net abc7.com
17 pagead2.googlesyndication.com scripts.webcontentassessor.com
pagead2.googlesyndication.com
ep2.adtrafficquality.google
www.googleadservices.com
16 cmp-abcotv.media.dssott.com abc7.com
15 cm.g.doubleclick.net 10 redirects abc7.com
google-bidout-d.openx.net
ssum.casalemedia.com
14 images.taboola.com
12 dsum-sec.casalemedia.com 1 redirects ssum.casalemedia.com
11 cdn.cookielaw.org dcf.espn.com
abc7.com
10 vidstat.taboola.com cdn.taboola.com
abc7.com
10 dcf.espn.com abc7.com
login.disney.com
9 pixel.rubiconproject.com 5 redirects
9 fonts.gstatic.com login.disney.com
fonts.googleapis.com
www.google.com
8 image8.pubmatic.com 7 redirects am-match.taboola.com
8 27f19c7c68e3eadf7756fb7efdb661dd8909acf9.cws.conviva.com abc7.com
8 www.googleadservices.com scripts.webcontentassessor.com
www.googleadservices.com
8 match.adsrvr.org 8 redirects
8 log.go.com abc7.com
login.disney.com
8 trc.taboola.com abc7.com
cdn.taboola.com
7 sync.taboola.com ssum.casalemedia.com
am-match.taboola.com
6 token.rubiconproject.com 4 redirects eus.rubiconproject.com
6 cdn.taboola.com abc7.com
5 creativecdn.com 5 redirects
5 browser-intake-datadoghq.com login.disney.com
5 eu.asas.yango.com abc7.com
display.asas.yango.tech
5 pcs.bamgrid.com abc7.com
5 s.abcnews.com abc7.com
assets-cdn.abcotvs.net
4 prebid-server.rubiconproject.com abc7.com
4 abcotv.hb-api.omtrdc.net abc7.com
4 cdn-gl.imrworldwide.com abc7.com
4 eus.rubiconproject.com am-match.taboola.com
eus.rubiconproject.com
4 www.gstatic.com www.google.com
www.gstatic.com
4 sdk.iad-05.braze.com abc7.com
4 sw88.go.com abc7.com
4 il-trc-events.taboola.com cdn.taboola.com
4 sb.scorecardresearch.com 2 redirects
4 securepubads.g.doubleclick.net abc7.com
4 hiveplayer-static.bamgrid.com abc7.com
4 cdn.abcotvs.com abc7.com
3 x.bidswitch.net 3 redirects
3 image2.pubmatic.com 3 redirects
3 pixel.tapad.com 2 redirects
3 match.prod.bidr.io 3 redirects
3 s.amazon-adsystem.com 1 redirects
3 am-vid-events.taboola.com vidstat.taboola.com
3 ssum.casalemedia.com 1 redirects am-match.taboola.com
3 data.ad-score.com abc7.com
3 c1.adform.net 3 redirects
3 us-u.openx.net google-bidout-d.openx.net
3 tpc.googlesyndication.com scripts.webcontentassessor.com
3 display.asas.yango.tech scripts.webcontentassessor.com
display.asas.yango.tech
3 ep2.adtrafficquality.google abc7.com
3 ib.adnxs.com 1 redirects
3 www.google.com login.disney.com
abc7.com
www.gstatic.com
3 disney-entertainment.api.edge.bamgrid.com abc7.com
3 mab.chartbeat.com abc7.com
3 bam.nr-data.net abc7.com
3 siteintercept.qualtrics.com abc7.com
3 abc7.com 1 redirects
2 disney-entertainment.connections.edge.bamgrid.com
2 pixel-sync.sitescout.com 2 redirects
2 sync-tm.everesttech.net 1 redirects ssum.casalemedia.com
2 census-web.scorecardresearch.com
2 aax-eu.amazon-adsystem.com 1 redirects
2 pixel-us-east.rubiconproject.com 2 redirects
2 disney-entertainment.playback.edge.bamgrid.com abc7.com
2 wf.taboola.com abc7.com
2 imprammp.taboola.com abc7.com
2 am-match.taboola.com abc7.com
2 rtb.openx.net 1 redirects
2 js.ad-score.com abc7.com
2 cdn.registerdisney.go.com login.disney.com
2 fonts.googleapis.com abc7.com
2 ep1.adtrafficquality.google abc7.com
2 gum.criteo.com 1 redirects
2 www.googletagservices.com abc7.com
www.googleadservices.com
2 ping.chartbeat.net
2 tru.am abc7.com
2 static.chartbeat.com abc7.com
1 d.adroll.com 1 redirects
1 dsum.casalemedia.com ssum.casalemedia.com
1 p.rfihub.com 1 redirects
1 trace.mediago.io 1 redirects
1 www.temu.com ssum.casalemedia.com
1 tskekwqpdovdxtqtskdeycqal9hwq1788722137.nuid.imrworldwide.com
1 simage2.pubmatic.com 1 redirects
1 image4.pubmatic.com 1 redirects
1 capi.connatix.com
1 sync.ipredictive.com 1 redirects
1 sync.a-mo.net
1 px.ads.linkedin.com
1 linear-abcotv-akc-na-east-1.media.dssott.com abc7.com
1 cm.ctnsnet.com 1 redirects
1 gw-iad-bid.ymmobi.com 1 redirects
1 s.company-target.com 1 redirects
1 ssum-sec.casalemedia.com 1 redirects
1 watch.auth.api.espn.com abc7.com
1 favicon.asas.yango.tech abc7.com
1 avatars.asas.yango.tech abc7.com
1 eu-u.openx.net google-bidout-d.openx.net
1 ups.analytics.yahoo.com abc7.com
ssum.casalemedia.com
1 google-bidout-d.openx.net abc7.com
1 id5-sync.com abc7.com
1 sync6.im-apps.net abc7.com
1 ident.mygaru.com abc7.com
1 spadsync.com abc7.com
1 bcp.crwdcntrl.net abc7.com
1 cds.taboola.com abc7.com
1 0c94aa5156cf0935a827c3b9863ae691.safeframe.googlesyndication.com abc7.com
1 invstatic101.creativecdn.com abc7.com
1 cdn.mgaru.dev abc7.com
1 connectid.analytics.yahoo.com abc7.com
1 cdn.jsdelivr.net abc7.com
1 dmp.im-apps.net abc7.com
1 cdn.id5-sync.com abc7.com
1 ads.pubmatic.com abc7.com
1 cdn.fusion-platform.com abc7.com
1 oa.openxcdn.net abc7.com
1 tags.crwdcntrl.net abc7.com
1 secure.espncdn.com abc7.com
1 disney.demdex.net abc7.com
1 secure.espn.com abc7.com
1 js.appboycdn.com abc7.com
1 beacon.tru.am abc7.com
1 client-sdk-configs.bamgrid.com abc7.com
1 cdn.disneyaccount.com abc7.com
1 api.abcotvs.com abc7.com
1 zn5hsliyrlhlj7ndr-abcotv.siteintercept.qualtrics.com abc7.com
1 js-agent.newrelic.com abc7.com
1 pinpoint.espn.com abc7.com
1 scripts.webcontentassessor.com abc7.com
0 8r4gmjpf7oh1f4k6kvliwheufdaa51788722132.nuid.imrworldwide.com Failed
0 ofobcf0jnrxzvhgar1o4dqljwayhw1788722132.nuid.imrworldwide.com Failed
0 secure-dcr.imrworldwide.com Failed
0 id.rlcdn.com Failed
0 playback-certs.bamgrid.com Failed abc7.com
0 linear-abcotv-ftc-na-east-1.media.dssott.com Failed abc7.com
0 static-assets.bamgrid.com Failed abc7.com
0 27f19c7c68e3eadf7756fb7efdb661dd8909acf9.ipv6.cws.conviva.com Failed abc7.com
0 27f19c7c68e3eadf7756fb7efdb661dd8909acf9.ipv4.cws.conviva.com Failed abc7.com
0 prod.gatekeeper.us-abc.symphony.edgedatg.go.com Failed abc7.com
0 cdn.espn.com Failed dcf.espn.com
0 cdn.abcotvs.net Failed abc7.com
667 142
Subject Issuer Validity Valid
abc7.com
Amazon RSA 2048 M04
2026-08-07 -
2027-02-20
7mo crt.sh
editions.geo.hosted.abcotvs.com
Amazon RSA 2048 M04
2025-11-03 -
2026-12-02
1yr crt.sh
dcf.espn.com
Sectigo Public Server Authentication CA OV R36
2026-03-18 -
2026-10-02
7mo crt.sh
s.abcnews.com
Amazon RSA 2048 M01
2026-07-24 -
2027-02-06
7mo crt.sh
*.webcontentassessor.com
Amazon RSA 2048 M04
2025-10-16 -
2026-11-13
1yr crt.sh
cookielaw.org
WE1
2026-07-22 -
2026-10-20
3mo crt.sh
www.espn.com
Sectigo Public Server Authentication CA OV R36
2026-04-21 -
2026-11-05
7mo crt.sh
*.bamgrid.com
Amazon RSA 2048 M01
2026-05-25 -
2026-12-08
7mo crt.sh
js-agent.newrelic.com
GlobalSign Atlas R3 DV TLS CA 2025 Q4
2025-11-25 -
2026-12-27
1yr crt.sh
*.qualtrics.com
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2025-12-04 -
2026-12-02
1yr crt.sh
*.nr-data.net
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2026-03-13 -
2026-09-27
7mo crt.sh
api.abcotvs.com
Amazon RSA 2048 M04
2026-08-25 -
2027-03-10
7mo crt.sh
*.disneyaccount.com
Amazon RSA 2048 M01
2025-12-14 -
2027-01-12
1yr crt.sh
*.chartbeat.com
Thawte TLS RSA CA G1
2026-05-18 -
2026-12-02
7mo crt.sh
*.taboola.com
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2025-12-15 -
2027-01-05
1yr crt.sh
tru.am
WE1
2026-08-22 -
2026-11-20
3mo crt.sh
*.chartbeat.net
Thawte TLS RSA CA G1
2025-12-11 -
2026-12-29
1yr crt.sh
*.g.doubleclick.net
WE2
2026-08-10 -
2026-11-02
3mo crt.sh
login.disney.com
Amazon RSA 2048 M04
2026-04-07 -
2026-10-21
7mo crt.sh
*.api.edge.bamgrid.com
Amazon RSA 2048 M04
2026-04-18 -
2026-11-01
7mo crt.sh
appboycdn.com
WE1
2026-07-18 -
2026-10-16
3mo crt.sh
a.espncdn.com
YR1
2026-08-17 -
2026-11-15
3mo crt.sh
*.demdex.com
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2025-10-14 -
2026-11-14
1yr crt.sh
log.go.com
Amazon RSA 2048 M04
2026-07-24 -
2027-02-06
7mo crt.sh
sw88.go.com
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2025-10-10 -
2026-11-10
1yr crt.sh
*.google.com
WR2
2026-08-10 -
2026-11-02
3mo crt.sh
sdk.iad-05.braze.com
WE1
2026-07-24 -
2026-10-22
3mo crt.sh
adtrafficquality.google
WE2
2026-08-10 -
2026-11-02
3mo crt.sh
*.crwdcntrl.net
Amazon RSA 2048 M04
2026-07-10 -
2027-01-23
7mo crt.sh
oa.openxcdn.net
WR3
2026-08-02 -
2026-10-31
3mo crt.sh
cdn.prod.novatiq.com
Amazon RSA 2048 M04
2025-11-25 -
2026-12-24
1yr crt.sh
*.pubmatic.com
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2025-10-02 -
2026-10-01
1yr crt.sh
id5-sync.com
WE1
2026-07-12 -
2026-10-10
3mo crt.sh
*.im-apps.net
DigiCert Global G3 TLS ECC SHA384 2020 CA1
2025-12-19 -
2026-12-19
1yr crt.sh
*.jsdelivr.net
Sectigo Public Server Authentication CA DV R36
2026-04-22 -
2026-11-06
7mo crt.sh
connectid.analytics.yahoo.com
GlobalSign ECC OV SSL CA 2018
2026-06-09 -
2026-12-03
6mo crt.sh
mgaru.dev
WE1
2026-08-26 -
2026-11-24
3mo crt.sh
invstatic101.creativecdn.com
WR3
2026-09-02 -
2026-12-01
3mo crt.sh
upload.video.google.com
WE2
2026-08-10 -
2026-11-02
3mo crt.sh
cdn.registerdisney.go.com
Sectigo Public Server Authentication CA OV E36
2026-02-02 -
2027-02-02
1yr crt.sh
*.gstatic.com
WE2
2026-08-10 -
2026-11-02
3mo crt.sh
*.ad-score.com
Go Daddy Secure Certificate Authority - G2
2025-09-06 -
2026-10-08
1yr crt.sh
eu.asas.yango.com
GlobalSign GCC R3 DV TLS CA 2020
2026-07-17 -
2027-01-15
6mo crt.sh
1722199366.rsc.cdn77.org
YE1
2026-08-06 -
2026-11-04
3mo crt.sh
tpc.googlesyndication.com
WE2
2026-08-10 -
2026-11-02
3mo crt.sh
spadsync.com
Go Daddy Secure Certificate Authority - G2
2026-02-22 -
2027-03-26
1yr crt.sh
ident.mygaru.com
YE2
2026-08-08 -
2026-11-06
3mo crt.sh
*.browser-intake-datadoghq.com
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2026-01-06 -
2027-01-11
1yr crt.sh
*.openx.net
RapidSSL TLS RSA CA G1
2026-07-18 -
2027-02-01
7mo crt.sh
*.pubgw.ads.yahoo.com
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2026-08-17 -
2026-10-07
2mo crt.sh
1337028965.rsc.cdn77.org
YE1
2026-08-06 -
2026-11-04
3mo crt.sh
1410583013.rsc.cdn77.org
YE1
2026-08-06 -
2026-11-04
3mo crt.sh
*.rubiconproject.com
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2026-03-25 -
2026-09-30
6mo crt.sh
casalemedia.com
YE2
2026-07-24 -
2026-10-22
3mo crt.sh
*.playback.edge.bamgrid.com
Amazon RSA 2048 M04
2026-04-18 -
2026-11-01
7mo crt.sh
*.imrworldwide.com
GlobalSign RSA OV SSL CA 2018
2026-01-19 -
2027-02-20
1yr crt.sh
cdn1.edgedatg.com
YR2
2026-08-05 -
2026-11-03
3mo crt.sh
*.hb-api.omtrdc.net
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2026-04-28 -
2026-11-12
7mo crt.sh
cws.conviva.com
Sectigo Public Server Authentication CA OV R36
2026-01-19 -
2027-02-08
1yr crt.sh
*.media.dssott.com
COMODO RSA Organization Validation Secure Server CA
2025-11-14 -
2026-11-14
1yr crt.sh
*.scorecardresearch.com
Sectigo Public Server Authentication CA DV R36
2026-04-06 -
2026-10-21
7mo crt.sh
*.nuid.imrworldwide.com
Amazon RSA 2048 M04
2026-08-25 -
2027-03-10
7mo crt.sh
*.temu.com
GoDaddy TLS Intermediate CA DV - R1v1
2026-07-15 -
2027-01-29
7mo crt.sh

This page contains 22 frames:

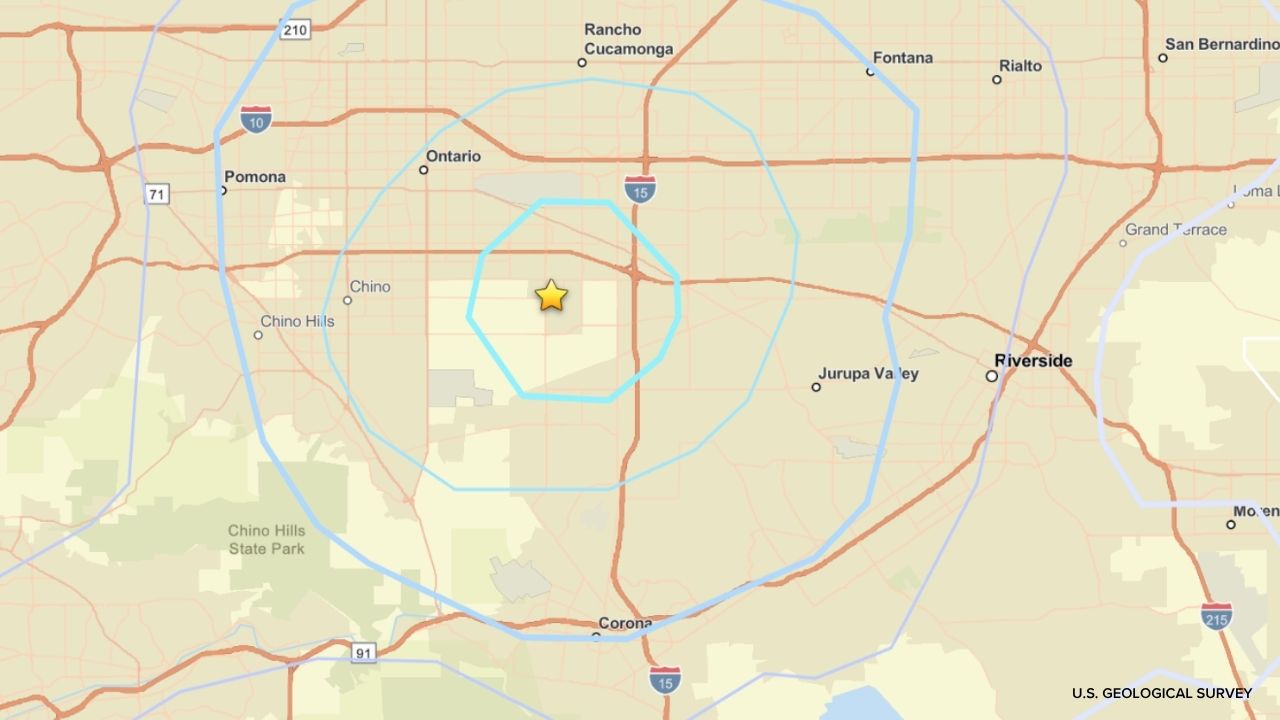
Primary Page: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Frame ID: 1398E22742853BD7C37197FC06FEF582
Requests: 290 HTTP requests in this frame

Frame: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Frame ID: 47305B5FFA90CBECB41766A8E4AF5301
Requests: 248 HTTP requests in this frame

Frame: https://ib.adnxs.com/bounce?%2Fsetuid%3Fentity%3D584%26code%3D419acdb7-b09e-4b32-b034-56c31d5fd705-tuct11974151%26gdpr%3D0%26gdpr_consent%3D
Frame ID: D03C341EC3F4F56C4A6E6A9EA5AFE8D8
Requests: 2 HTTP requests in this frame

Frame: https://cm.g.doubleclick.net/partnerpixels?gpp=DBABLA~BVQqAAAAAAJY.QA&gpp_sid=7&url=https%3A%2F%2Fabc7.com%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F
Frame ID: E284C65252B978B73583BEAFD6E8B00A
Requests: 1 HTTP requests in this frame

Frame: https://0c94aa5156cf0935a827c3b9863ae691.safeframe.googlesyndication.com/safeframe/1-0-45/html/container.html
Frame ID: CD6ADD1912B5860A4A2208E18886CC5F
Requests: 1 HTTP requests in this frame

Frame: https://securepubads.g.doubleclick.net/pagead/adview?ai=CY81f0rudaoDxJP-EmNAP7LajwAac3IGXhwHf1JOirRbAjbcBEAEgkvrgb2D5uvSDnBDIAQngAgCoAwHIAwKqBIADT9CNMjjqNnztRarE9rPkInz6pLvZxn_yHLOM6z-idDO-8_qr7Mmg9elX8XHlwCyJhx4h7-1tLgNcL6H6TET1nMvlaZKjeZdyeatzrsbgq6p1jm7XTLXpznA0PKvDdiIIFo9n6BXphze_9-9ZJfmxPUM0iT4FWr-SLj7ulpialfV9AVV-co_8OXs6Sb-d-fCJBB3StFOY1oythTdOxKEW1cG5NDYgXW4E5pXRnZ0loh1LkszRF0Gv8ByVzGwFLDzHbT-xfzQmPWxqxKA6G__-vqBU_Sqr18Qm7483OOs8g3DfD4OKfkZvfVStv9xrElcHcTTggHNcjFJw52k-2g1eteHkTXmABCVcnhdCbF5PpmEanE61g5NlRB5NkW48G_bKsSfp84j1rkV_3Z87D1EneHa8hLZ8RdWSWTyZ7asU4Xw_DGnF50ukdHJb5pVcxTAzqJSOaEscVXeLFwDjh4jRzZmcg53vPPc8t-2Q1yHZ1xdqyouuIDbo2XEFBxjToDDx4AQBgAavp5DL_8K4_UygBiGoB5PYsQKoB5TYsQKoB5XYsQKoB6a-G6gHltgbqAeqm7ECqAf_nrECqAffn7ECqAf-6LECqAetvrEC2AcA0ggwCIBhEAEyCIqCgICAgIAIOg-AQIDAgICAgKiAAqiDkBBIvf3BOljuzMaZ1dqWA2AAgAoD-gsCCAGADAGqDQJJTOINEwjmoseZ1dqWAxV_AgYEHWzbCGjqDRMI44PImdXalgMVfwIGBB1s2whoiA7___________8B0BUBgBcBshcsChoSFHB1Yi03MTU0ODc5NjUxOTkyNjIxGNvHbxgMKgo0MDM2NjAxMTMwUAGqGBcJ43oUrgdAv0ASCjQwMzY2MDExMzAYAQ&sigh=LA2IjG5HxsQ&uach_m=%5BUACH%5D&sreq=1&cid=CAQShwIAQM4h3PIgp1aO-yYQmCiFcqHJ7Z_e9ztBjXcKcmDzfvPwRD_Pqp8LeiCksp5dFpuzWGKMV881n4dSmlA1OB6axy1On9oEERjGCN6ZpFZi9QMy88x105xTqM3Uj8qo3WLZh94tsdswcieENYt1ynlYp-A-7gYPnr9Y6S85ZktvqTyNY83ybGuvKxyZY7s9Kz59tQIs8PB5cpzCDu8ZWjyCciB8n1uEQuB6cZEBvL6Zq_hnFG-HfOLnMCgObBHTIuq4Cnr9MYrrz1BWrSJaiWbyel0pkSNd0IYcw4Qq7DQuZa2HBcj65J-0aqHWYjGBVR9hy6qHqUbMnqPxmm0TR127W6BTGKy2hhgB
Frame ID: 595B7AA4EC70E07C5A535F6F6F85B100
Requests: 21 HTTP requests in this frame

Frame: https://am-match.taboola.com/sync?dast=V9kekCABYDAOCg-NNdmUJrBADgoPjTXZlCawUAAAAABgYAawcAJLRwuTymhcOt3GxGa9FuNlsLdxvLWrAaTpyDwWTiMk2GAEBCC5fLY1o43MrNZrQW7WaztXC3sawFq-HEORhMJi7TZAoAH8ZymQxqgYRl9vsOCsrp6TG7DKKi622xO5xmzxsA4tB0Onyue73C4vHNNX63X_D3nP6a0Vrt8NmdptfJ5VY5LKej4_XwutxCp-nz1ttND8vT79YcHV6n3eeWucymt-Zhd0tclrvDcnLa_W6N33U3Pd-qz8_z1jycn79iudstd4vJXg4AAAAAAA8A_____xAAAAAAABEAAAAAABIAAAAAABQAARUA_xYAAhcAAAAAABgA_____xoAAGcbAALUIAcAAr3MBoXtafsHAAAAAAAIAAAAAAAJAAAAAEAJAAAAAMAJwP________9_DMAAfeaNDMD_____DYBBDwDAgw8AwIMQAAAAQMgQwH8BxoD0hKYkEQCAwEhcEYAjgEkAnQBQAVhUAfz___dbAQBcAQAABIDilaxuZAHoDkq8hQEAAAAMjAEs0MPi95sddo3f7TKA_________38zgP8zgH80ACGAI9c0AKEFD1w1gF9AAIA1gF9AAAA2AHUD-P9_AwiAAwg7AAAAAIA7gP___389AJBbGBbD0cQ0MoxGi-XIOXPZTKaFZznYbYyjhXPhPYAcck6P7aJG8D6ACmuaXH6DpOUyGxQUv-1lkLFcJvsBTNhitJpMNsvhbLmYDIaj4Wi0P4CBWE0GCEDRksVqOVztJovRZrGYLHfD0WSCABQtGkxWo9FkMRmuRpPVbLnY7TYIQNGq1Wy0GQxXs8lst1sNB8PlaIQAE7YYrSaTzXI4Wy4mg-FoOBoNESCGFsuFx2TxrSWG5cotmngma4lhM1qrZhvPYuSamXyD1Vr0-pgei-VutFgttgggGHC4F8nTIp3INp6RxeIbOWYmw2YwW-yGy4nF5HKYhsvRxLjYWMQSzckincgu-97CsBiOJqaRYTRaLEfOmctmMi08y8FuYxwtnAt_abFceEwW31piWK7coolnspYYNqO1arbxLEaumck3WK1Fr4_psVjuRovVYt_YDYe7yWQxWe4bu-FwN5ksJst9h87wXX3ORmc1MvPo1FfZ8yPSOQwKl8HiXatOJ213eHCuDEanTP1UFnRGv9_v9_v9fr_f7zdoPQezQeE75xzG77j8knar5cfBYzAYHSaD0WE0GA2KWCK4SCcKi8dvuv1eFrfC4vGNHRaxRGm6SCd6wd9z-mtGa7XDZ3eaXieXW-WwnI6O18Prcgudps9bbzc9LE-_W3N0eJ12n1vmMpvemofdLXFZ7g7LyWn3uzV-1930fKs-P89b83B-_orlbrfcLSYTsURwukgnopfxdFG_EgAAAAAAAAAAwBLAJgAAAAAAJ0AALBcAQGL5WxcAGAQAAAAAAGAXIBoFS0e0tXDrGAAiLB6_6fZ7WdwKi8c3dlgZAEAiVpIZYDPAZwCCmNPZsgYAAAAQwAYAAAAo4wbYDcAbQIAaHAf4___3pwcAAABY2wcAYgo8cqXQC-cHKJjJajTYPwCAAIWY09nqdmNOZysgoCAGm9FgAgH_____BAEAAAAAAAB_HAgBAttuQgCFAIMhWv5ulxcCOgQA2AkqRnvCkz4EAAAEgOKVqHJBBFgQhUEhM-gXWqPxYDAYDAaVWVc0GBEQcJsIQLDVbrgbCFajCPj___-vCFhIBoUxGSsZFMZqFgEAdoKK0q9FLhcBAAABoHglqGgYAQ0x3M0Vq7liMpzLVtMIACjjCCAgFqdLjwA!&excid=22&docw=0&cijs=1&nlb=false
Frame ID: 787760C9B7B9C7926DAD1DAD3B777D99
Requests: 4 HTTP requests in this frame

Frame: https://imprammp.taboola.com/st?cijs=convusmp&ttype=0&cisd=convusmp&cipid=66361655&crid=-1&dast=V9FjsCABYDAOCg-NNdmUJrBADgoPjTXZlCawUAAAAABgYA9AcAJDmYGEYT02qtm7hMa9FyM1tLfBPjWrOyuCzG3WZlswyGAECSg4lhNDGt1rqJy7QWLTeztcQ3Ma41K4vLYtxtVjbLYAoAH8ZymQxqgYRl9vsOCsrp6TG7DKKi622xO5xmzxsA4tB0Onyue73C4vHNNX63X_D3nP6a0Vrt8NmdptfJ5VY5LKej4_XwutxCp-nz1ttND8vT79YcHV6n3eeWucymt-Zhd0tclrvDcnLa_W6N33U3Pd-qz8_z1jycn79iudstd4vJXg4AAAAAAA8A_____xAAAAAAABEAAAAAABIAAAAAABQAARUA_xYAAhcAAAAAABgA_____xoAAGcbAALUIAcAAr3MBoXtafsHAAAAAAAIAAAAAAAJAEBB-UwJAAAIysUJwP________9_DMAAfeaNDMD_____DYBBDwDAgw8AwIMQAAAAQMgQAIQHmcpkA5wqEQCAwIhXEYAjgEkAnQBQAVhUAfz___dbAQBcAQAABIDilayCZAHoDkq8hQEAAAAMjAEs0MPi95sddo3f7TKA_________38zgP8zgH80ACGAI9c0AKEFD1w1gF9AAIA1gF9AAAA2AHUD-P9_AwiAAwg7AAAAAIA7gP___389AJBbGBbD0cQ0MoxGi-XIOXPZTKaFZznYbYyjhXPhPYAcck6P7aJG8D6AEGGZ_b6DgnJ6eswug6joelvsDqfZcxAfNAzLySCYH8CELUaryWSzHM6Wi8lgOBqORvsDGIjVZIAAFC1ZrJbD1W6yGG0Wi8lyNxxNJghA0aLBZDUaTRaT4Wo0Wc2Wi91ugwAUrVrNRpvBcDWbzHa71XAwXI5GCDBhi9FqMtksh7PlYjIYjoaj0RABYmixXHhMFt9aYliu3KKJZ7KWGDajtWq28SxGrpnJN1itRa-P6bFY7kaL1WKLAIIBh3uRPC3SiWzjGVksvpFjZjJsBrPFbricWEwuh2m4HE2Mi41FLNGcLNKJ7LLvLQyL4WhiGhlGo8Vy5Jy5bCbTwrMc7DbG0cK58JcWy4XHZPGtJYblyi2aeCZriWEzWqtmG89i5JqZfIPVWvT6mB6L5W60WC32jd1wuJtMFpPlvrEbDneTyWKy3HfoDN_V52x0ViMzj059lT0_Ip3DoHAZLN616nTSdocH58pgdMrUT2VBZ_T7_X6_3-_3-_1-g9ZzMBsUvnPOYfyOyy9pt1p-HDwGg9FhMhgdRoPRoIglgot0orB4_Kbb72VxKywe39hhEUuUpot0ohf8Pae_ZrRWO3x2p-l1crlVDsvp6Hg9vC630Gn6vPV208Py9Ls1R4fXafe5ZS6z6a152N0Sl-XusJycdr9b43fdTc-36vPzvDUP5-evWO52y91iMhFLBKeLdCJ6GU8X9SsBAAAAAAAAAAAsAWwCAAAAAHACGMxwtlmt1glwIIvBbrRYLRcAQGL5WxcAGAQAAAAAAGAXIBoFS0e0tXDrGAAiLB6_6fZ7WdwKi8c3dlgZAEAiVpIZYDPAZwCCmNPZsgYAAAAQwAYAAAAo4wbYDcAbQIAaHAf4___3pwcAAACg3wcAghJ75EKpH-YHKJjJajTYPwCAAIWY09nqdmNOZysgoCAGm9FgAgH_____BAEAAAAAAAB_HAgBAttuQgCFAIMhWv5ulxcCOgQA2AkqRnvCkz4EAAAEgOKVqHJBBFgQhUEhM-gXWqPxYDAYDAaVWVc0GBEQcJsIQLDVbrgbCFajCPj___-vCFhIBoUxGSsZFMZqFgEAdoKK0q9FKBcBAAABoHglqGgYAQ0x3M0Vq7liMpzLVtMIACjjCCAgFqdLjwA!&cmcv=&pix=undefined&cb=1788722131068&uv=3624&tms=1788722131068&abt=ufm&ft=0&unm=FEED_MANAGER&aure=false&agl=101&cirid=90b04b45-7be4-4936-b7b8-3ebeb873ef20&excid=e22lLINE_ITEM_ID_WILL_BE_HERE_ON_SERVINGc&tst=1&docw=0&cs=true&cias=1
Frame ID: 54D347A8269B9A2D2604069B9105FE52
Requests: 1 HTTP requests in this frame

Frame: https://am-match.taboola.com/sync?dast=V9FjsCABYDAOCg-NNdmUJrBADgoPjTXZlCawUAAAAABgYA9AcAJDmYGEYT02qtm7hMa9FyM1tLfBPjWrOyuCzG3WZlswyGAECSg4lhNDGt1rqJy7QWLTeztcQ3Ma41K4vLYtxtVjbLYAoAH8ZymQxqgYRl9vsOCsrp6TG7DKKi622xO5xmzxsA4tB0Onyue73C4vHNNX63X_D3nP6a0Vrt8NmdptfJ5VY5LKej4_XwutxCp-nz1ttND8vT79YcHV6n3eeWucymt-Zhd0tclrvDcnLa_W6N33U3Pd-qz8_z1jycn79iudstd4vJXg4AAAAAAA8A_____xAAAAAAABEAAAAAABIAAAAAABQAARUA_xYAAhcAAAAAABgA_____xoAAGcbAALUIAcAAr3MBoXtafsHAAAAAAAIAAAAAAAJAEBB-UwJAAAIysUJwP________9_DMAAfeaNDMD_____DYBBDwDAgw8AwIMQAAAAQMgQAIQHmcpkA5wqEQCAwIhXEYAjgEkAnQBQAVhUAfz___dbAQBcAQAABIDilayCZAHoDkq8hQEAAAAMjAEs0MPi95sddo3f7TKA_________38zgP8zgH80ACGAI9c0AKEFD1w1gF9AAIA1gF9AAAA2AHUD-P9_AwiAAwg7AAAAAIA7gP___389AJBbGBbD0cQ0MoxGi-XIOXPZTKaFZznYbYyjhXPhPYAcck6P7aJG8D6AEGGZ_b6DgnJ6eswug6joelvsDqfZcxAfNAzLySCYH8CELUaryWSzHM6Wi8lgOBqORvsDGIjVZIAAFC1ZrJbD1W6yGG0Wi8lyNxxNJghA0aLBZDUaTRaT4Wo0Wc2Wi91ugwAUrVrNRpvBcDWbzHa71XAwXI5GCDBhi9FqMtksh7PlYjIYjoaj0RABYmixXHhMFt9aYliu3KKJZ7KWGDajtWq28SxGrpnJN1itRa-P6bFY7kaL1WKLAIIBh3uRPC3SiWzjGVksvpFjZjJsBrPFbricWEwuh2m4HE2Mi41FLNGcLNKJ7LLvLQyL4WhiGhlGo8Vy5Jy5bCbTwrMc7DbG0cK58JcWy4XHZPGtJYblyi2aeCZriWEzWqtmG89i5JqZfIPVWvT6mB6L5W60WC32jd1wuJtMFpPlvrEbDneTyWKy3HfoDN_V52x0ViMzj059lT0_Ip3DoHAZLN616nTSdocH58pgdMrUT2VBZ_T7_X6_3-_3-_1-g9ZzMBsUvnPOYfyOyy9pt1p-HDwGg9FhMhgdRoPRoIglgot0orB4_Kbb72VxKywe39hhEUuUpot0ohf8Pae_ZrRWO3x2p-l1crlVDsvp6Hg9vC630Gn6vPV208Py9Ls1R4fXafe5ZS6z6a152N0Sl-XusJycdr9b43fdTc-36vPzvDUP5-evWO52y91iMhFLBKeLdCJ6GU8X9SsBAAAAAAAAAAAsAWwCAAAAAHACGMxwtlmt1glwIIvBbrRYLRcAQGL5WxcAGAQAAAAAAGAXIBoFS0e0tXDrGAAiLB6_6fZ7WdwKi8c3dlgZAEAiVpIZYDPAZwCCmNPZsgYAAAAQwAYAAAAo4wbYDcAbQIAaHAf4___3pwcAAACg3wcAghJ75EKpH-YHKJjJajTYPwCAAIWY09nqdmNOZysgoCAGm9FgAgH_____BAEAAAAAAAB_HAgBAttuQgCFAIMhWv5ulxcCOgQA2AkqRnvCkz4EAAAEgOKVqHJBBFgQhUEhM-gXWqPxYDAYDAaVWVc0GBEQcJsIQLDVbrgbCFajCPj___-vCFhIBoUxGSsZFMZqFgEAdoKK0q9FKBcBAAABoHglqGgYAQ0x3M0Vq7liMpzLVtMIACjjCCAgFqdLjwA!&excid=22&docw=0&cijs=1&nlb=false
Frame ID: 5B9EC9CE8A676F7D53CA09956C2DC2E9
Requests: 4 HTTP requests in this frame

Frame: https://google-bidout-d.openx.net/w/1.0/pd?plm=5
Frame ID: 4B91B8020C1CC664B4E61C7427391DD5
Requests: 6 HTTP requests in this frame

Frame: https://ep2.adtrafficquality.google/sodar/sodar2/255/runner.html
Frame ID: F9782817EA725821E5351C14E4616BC1
Requests: 3 HTTP requests in this frame

Frame: https://www.google.com/recaptcha/api2/aframe
Frame ID: 61741B8C4F34C1FBFF643E6F4F08B5A3
Requests: 2 HTTP requests in this frame

Frame: https://www.googleadservices.com/pagead/managed/js/activeview/current/reach_worklet.html
Frame ID: 90E5B05972D74F83A1EFE1192224C64E
Requests: 18 HTTP requests in this frame

Frame: https://www.google.com/recaptcha/enterprise/anchor?ar=1&k=6LcnzusZAAAAABiX7zUG2lN9BBH_1ERH1pfyR95-&co=aHR0cHM6Ly9sb2dpbi5kaXNuZXkuY29tOjQ0Mw..&hl=iw&v=8x-4t2pegToiW8KmThtO4AQt&size=invisible&anchor-ms=20000&execute-ms=30000&cb=72ilyxa5gdw7
Frame ID: 344432F41B7C0010BB1BCCD1DBEB5EC5
Requests: 6 HTTP requests in this frame

Frame: https://eus.rubiconproject.com/usync.html?p=16698&endpoint=us-east&gdpr=0&us_privacy=1NN-
Frame ID: B2F102F805AF5FC36B8E92D35459E6C2
Requests: 20 HTTP requests in this frame

Frame: https://ssum.casalemedia.com/usermatch?cb=https%3A%2F%2Fsync.taboola.com%2Fsg%2Fcasale-network%2F1%2Frtb-h%2F%3Ftaboola_hm%3D%5Bpartner_user_id%5D%26orig%3Dvideo%26us_privacy%3D1NN-&gdpr=0&s=183756&us_privacy=1NN-&C=1
Frame ID: B9F8E859FD7986AD3542782B1166060F
Requests: 10 HTTP requests in this frame

Frame: data://truncated
Frame ID: 079E4BB8E11FD66491990732216E8273
Requests: 1 HTTP requests in this frame

Frame: https://eus.rubiconproject.com/usync.html?p=16698&endpoint=us-east&gdpr=0&us_privacy=1NN-
Frame ID: 194AEE2CF40E868CDFB8DEDDFF2C75E3
Requests: 4 HTTP requests in this frame

Frame: https://cdn-gl.imrworldwide.com/novms/html/ls.html
Frame ID: 33C3602C83BD10EDE027BE38E5985569
Requests: 14 HTTP requests in this frame

Frame: https://sync.taboola.com/sg/rtb-pubmatic-network/1/rtb-h?taboola_hm=15934B2C-AE30-4515-9CE0-02BC4EDC0B5E
Frame ID: 1F80297283D3E45F9AA4EF11D4F80042
Requests: 1 HTTP requests in this frame

Frame: https://image8.pubmatic.com/AdServer/ImgSync?sec=1&gdpr=0&gdpr_consent=&us_privacy=
Frame ID: 332ADD921175396917FBBC8982F44AB2
Requests: 1 HTTP requests in this frame

Frame: https://ssum.casalemedia.com/usermatch?gdpr=0&s=183756&us_privacy=1NN-&cb=https%3A%2F%2Fsync.taboola.com%2Fsg%2Fcasale-network%2F1%2Frtb-h%2F%3Ftaboola_hm%3D%5Bpartner_user_id%5D%26orig%3Dvideo%26us_privacy%3D1NN-
Frame ID: E95E1CE1D5E9BBB23925EF2EF1B2A3A3
Requests: 10 HTTP requests in this frame

Screenshot Go Pro

Only in urlscan Pro

Use the Visual Search feature to find pages with visually similar screenshots.
Click for more information
Free trials of urlscan Pro are available.

Page Title

3.4-magnitude earthquake hits Ontario, shaking felt across San Bernardino County, USGS says - ABC7 Los Angeles

Detected technologies

(UI frameworks)
Overall confidence: 100%
Detected patterns
  • (?:/|-)bootstrap(?:[^/]*?([0-9a-fA-F]{7,40}|[\d]+(?:\.[\d]+(?:\.[\d]+)?)?)|)[^/]*?(?:\.min)?\.js

(JavaScript frameworks)
Overall confidence: 100%
Detected patterns
  • <[^>]+data-react

(Analytics)
Overall confidence: 50%
Detected patterns
  • sp\.js

(Advertising)
Overall confidence: 100%
Detected patterns
  • \.amazon-adsystem\.com

(Advertising)
Overall confidence: 100%
Detected patterns
  • adnxs\.(?:net|com)

(Marketing automation)
Overall confidence: 100%
Detected patterns
  • js\.appboycdn\.com/web-sdk/([\d.]+)

(Analytics)
Overall confidence: 100%
Detected patterns
  • chartbeat\.js

(Security)
Overall confidence: 100%
Detected patterns

(Advertising)
Overall confidence: 100%
Detected patterns
  • tpc\.googlesyndication\.com/safeframe

(Advertising)
Overall confidence: 100%
Detected patterns
  • \.doubleclick\.net

(Advertising)
Overall confidence: 100%
Detected patterns
  • googletagservices\.com/tag/js/gpt(?:_mobile)?\.js

(Advertising)
Overall confidence: 100%
Detected patterns
  • googlesyndication\.com/

(Advertising)
Overall confidence: 100%
Detected patterns
  • googletagservices\.com/tag/js/gpt\.js

(Advertising)
Overall confidence: 100%
Detected patterns
  • ^https://(?:cdn\.)?id5-sync\.com/

(CDN)
Overall confidence: 100%
Detected patterns
  • cdn\.jsdelivr\.net

(Cookie compliance)
Overall confidence: 100%
Detected patterns
  • cdn\.cookielaw\.org
  • otSDKStub\.js

(Advertising)
Overall confidence: 100%
Detected patterns
  • https?://[^/]*\.openx\.net

(Advertising)
Overall confidence: 100%
Detected patterns
  • adnxs\.com/[^"]*(?:prebid|/pb\.js)

(Advertising)
Overall confidence: 100%
Detected patterns
  • https?://[^/]*\.pubmatic\.com

(Surveys)
Overall confidence: 100%
Detected patterns
  • \.qualtrics\.com/

(Security)
Overall confidence: 100%
Detected patterns
  • /recaptcha/(?:api|enterprise)\.js

(Advertising)
Overall confidence: 100%
Detected patterns
  • https?://[^/]*\.rubiconproject\.com

(Advertising)
Overall confidence: 100%
Detected patterns
  • \.taboola\.com

Page Statistics

667
Requests

83 %
HTTPS

0 %
IPv6

76
Domains

142
Subdomains

101
IPs

12
Countries

11379 kB
Transfer

33048 kB
Size

114
Cookies

Redirected requests

There were HTTP redirect chains for the following requests:

Request Chain 69
  • https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/kabc HTTP 302
  • https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/kabc/
Request Chain 93
  • https://gum.criteo.com/sync?c=72&r=2&j=TRC.getRTUS HTTP 302
  • https://gum.criteo.com/sync?s=1&c=72&r=2&j=TRC.getRTUS
Request Chain 112
  • https://sb.scorecardresearch.com/cs/3000032/beacon.js HTTP 302
  • https://sb.scorecardresearch.com/internal-cs/default/beacon.js
Request Chain 173
  • https://ib.adnxs.com/setuid?entity=584&code=419acdb7-b09e-4b32-b034-56c31d5fd705-tuct11974151&gdpr=0&gdpr_consent= HTTP 307
  • https://ib.adnxs.com/bounce?%2Fsetuid%3Fentity%3D584%26code%3D419acdb7-b09e-4b32-b034-56c31d5fd705-tuct11974151%26gdpr%3D0%26gdpr_consent%3D
Request Chain 174
  • https://cm.g.doubleclick.net/pixel?google_nid=realize&google_hm=NDE5YWNkYjctYjA5ZS00YjMyLWIwMzQtNTZjMzFkNWZkNzA1LXR1Y3QxMTk3NDE1MQ&google_cm&&gdpr=0&gdpr_consent=&ui=419acdb7-b09e-4b32-b034-56c31d5fd705-tuct11974151 HTTP 302
  • https://cm.g.doubleclick.net/pixel?google_nid=realize&google_hm=NDE5YWNkYjctYjA5ZS00YjMyLWIwMzQtNTZjMzFkNWZkNzA1LXR1Y3QxMTk3NDE1MQ&google_cm=&gdpr=0&gdpr_consent=&ui=419acdb7-b09e-4b32-b034-56c31d5fd705-tuct11974151&google_tc= HTTP 302
  • https://trc.taboola.com/sg/google-authorized-buyers/1/um?gdpr=0&gdpr_consent=&ui=419acdb7-b09e-4b32-b034-56c31d5fd705-tuct11974151&google_gid=CAESED3a9cgUGsYhC81Z3AzTpUE&google_cver=1
Request Chain 193
  • https://sb.scorecardresearch.com/b?c1=2&c2=3000032&cs_fpcu=b49559bb63a0492fa9326a9ab40a120b&cs_it=b1&cv=4.13.1%2B2508250908&ns__t=1788722130539&ns_c=UTF-8&cs_cfg=1101110&cs_ucc=1&cs_cmp_id=28&gpp_ssv=1&gpp_gpc=0&gpp_oos=222&gpp_oon=1X11100&gpp_sdp=0000000000000000&gpp_pdc=2&gpp_cdc=000&gpp_mct=1&gpp_mom=1&gpp_msm=2&cs_cmp_ie=10&cs_cmp_rt=0&cs_cmp_av=1.1&gpp_sid=7&gpp_smv=1.1&c7=https%3A%2F%2Fabc7.com%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F&c8=3.4-magnitude%20earthquake%20hits%20Ontario%2C%20shaking%20felt%20across%20San%20Bernardino%20County%2C%20USGS%20says%20-%20ABC7%20Los%20Angeles&c9= HTTP 302
  • https://sb.scorecardresearch.com/b2?c1=2&c2=3000032&cs_fpcu=b49559bb63a0492fa9326a9ab40a120b&cs_it=b1&cv=4.13.1%2B2508250908&ns__t=1788722130539&ns_c=UTF-8&cs_cfg=1101110&cs_ucc=1&cs_cmp_id=28&gpp_ssv=1&gpp_gpc=0&gpp_oos=222&gpp_oon=1X11100&gpp_sdp=0000000000000000&gpp_pdc=2&gpp_cdc=000&gpp_mct=1&gpp_mom=1&gpp_msm=2&cs_cmp_ie=10&cs_cmp_rt=0&cs_cmp_av=1.1&gpp_sid=7&gpp_smv=1.1&c7=https%3A%2F%2Fabc7.com%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F&c8=3.4-magnitude%20earthquake%20hits%20Ontario%2C%20shaking%20felt%20across%20San%20Bernardino%20County%2C%20USGS%20says%20-%20ABC7%20Los%20Angeles&c9=
Request Chain 222
  • https://rtb.openx.net/esp?url=https%3A%2F%2Fabc7.com%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F&rid=esp HTTP 302
  • https://rtb.openx.net/esp?url=https%3A%2F%2Fabc7.com%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F&rid=esp&cc=1
Request Chain 331
  • https://cm.g.doubleclick.net/pixel?google_nid=openx&google_cm&google_sc HTTP 302
  • https://us-u.openx.net/w/1.0/sd?id=537072991&val=CAESEPNwFXcWM5XCcV-Nc7mMgpo&google_cver=1
Request Chain 333
  • https://match.adsrvr.org/track/cmf/openx?oxid=b2b48745-33f2-746c-cbd0-741212f6fa9d&gdpr=0 HTTP 302
  • https://match.adsrvr.org/track/cmb/openx?oxid=b2b48745-33f2-746c-cbd0-741212f6fa9d&gdpr=0 HTTP 302
  • https://us-u.openx.net/w/1.0/sd?id=537072971&val=854f06c6-0e88-4afd-a936-6a879ff410f4&ttd_puid=b2b48745-33f2-746c-cbd0-741212f6fa9d&gdpr=0&gdpr_consent=
Request Chain 334
  • https://creativecdn.com/cm-notify?pi=openx&gdpr=0 HTTP 302
  • https://creativecdn.com/cm-notify?pi=openx&gdpr=0&tc=1 HTTP 302
  • https://us-u.openx.net/w/1.0/sd?id=537073053&val=rhvrGoZzJvZi2sQgRiU87MebV0cruRe4rSwCGZyXCtY&pi=openx&gdpr=0&tc=1
Request Chain 335
  • https://c1.adform.net/serving/cookie/match?party=22 HTTP 302
  • https://c1.adform.net/serving/cookie/match?CC=1&party=22 HTTP 302
  • https://eu-u.openx.net/w/1.0/sd?id=537113484&val=4965478313182929533
Request Chain 349
  • https://ssum.casalemedia.com/usermatch?gdpr=0&s=183756&us_privacy=1NN-&cb=https%3A%2F%2Fsync.taboola.com%2Fsg%2Fcasale-network%2F1%2Frtb-h%2F%3Ftaboola_hm%3D%5Bpartner_user_id%5D%26orig%3Dvideo%26us_privacy%3D1NN- HTTP 302
  • https://ssum.casalemedia.com/usermatch?cb=https%3A%2F%2Fsync.taboola.com%2Fsg%2Fcasale-network%2F1%2Frtb-h%2F%3Ftaboola_hm%3D%5Bpartner_user_id%5D%26orig%3Dvideo%26us_privacy%3D1NN-&gdpr=0&s=183756&us_privacy=1NN-&C=1
Request Chain 350
  • https://match.adsrvr.org/track/cmf/generic?gdpr=0&ttd_pid=054f32o&us_privacy=1NN-&ttd_tpi=1 HTTP 302
  • https://match.adsrvr.org/track/cmb/generic?gdpr=0&ttd_pid=054f32o&us_privacy=1NN-&ttd_tpi=1 HTTP 302
  • https://trc.taboola.com/sg/thetradedesk-network/1/rtb-h/?taboola_hm=854f06c6-0e88-4afd-a936-6a879ff410f4
Request Chain 366
  • https://match.adsrvr.org/track/cmf/generic?gdpr=0&ttd_pid=054f32o&us_privacy=1NN-&ttd_tpi=1 HTTP 302
  • https://trc.taboola.com/sg/thetradedesk-network/1/rtb-h/?taboola_hm=854f06c6-0e88-4afd-a936-6a879ff410f4
Request Chain 437
  • https://match.adsrvr.org/track/cmf/casale HTTP 302
  • https://dsum-sec.casalemedia.com/rum?cm_dsp_id=39&external_user_id=854f06c6-0e88-4afd-a936-6a879ff410f4&expiration=1791314132&gdpr=0&gdpr_consent=
Request Chain 438
  • https://dsum-sec.casalemedia.com/rrum?ixi=1&cm_dsp_id=85&cb=https%3A%2F%2Fcm.g.doubleclick.net%2Fpixel%3Fgoogle_nid%3Dcasale_media2_dbm%26google_cm%26google_sc%26google_hm%3D HTTP 302
  • https://cm.g.doubleclick.net/pixel?google_nid=casale_media2_dbm&google_cm&google_sc&google_hm=ap271IsFVmMAGoX8ABrpggAA HTTP 302
  • https://dsum-sec.casalemedia.com/crum?cm_dsp_id=45&external_user_id=CAESELe28SzEDn8Iu3ee6Lg1yNU&google_cver=1
Request Chain 440
  • https://cm.g.doubleclick.net/pixel?google_nid=index&google_cm&google_hm=ap271IsFVmMAGoX8ABrpggAAE5sAAAAB&gdpr_consent=&us_privacy=&gdpr=&gpp=&gpp_sid= HTTP 302
  • https://ssum-sec.casalemedia.com/usermatchredir?s=184023&cb=https%3A%2F%2Fcm.g.doubleclick.net%2Fpixel%3Fgoogle_nid%3Dindex%26google_hm%3D&gdpr_consent=&gdpr=&gpp=&gpp_sid=&google_gid=CAESEAvKEcOUZ5Lma4-8ldIsXm0&google_cver=1 HTTP 302
  • https://cm.g.doubleclick.net/pixel?gdpr=&gdpr_consent=&google_cver=1&google_gid=CAESEAvKEcOUZ5Lma4-8ldIsXm0&google_hm=ap271IsFVmMAGoX8ABrpggAAE5sAAAAB&google_nid=index&gpp=&gpp=&gpp_sid=&gpp_sid=
Request Chain 441
  • https://creativecdn.com/cm-notify?pi=index&gpdr=&gdpr_consent=&us_privacy=&user_id=ap271IsFVmMAGoX8ABrpggAA%265019&gpp=&gpp_sid= HTTP 302
  • https://dsum-sec.casalemedia.com/crum?cm_dsp_id=133&external_user_id=rhvrGoZzJvZi2sQgRiU87MebV0cruRe4rSwCGZyXCtY&pi=index&gpdr=&gdpr_consent=&us_privacy=&user_id=ap271IsFVmMAGoX8ABrpggAA%265019&gpp=&gpp_sid=
Request Chain 442
  • https://s.company-target.com/s/ix?cm_dsp_id=18&us_privacy=&gdpr=&gdpr_consent=&gpp=&gpp_sid= HTTP 302
  • https://dsum-sec.casalemedia.com/crum?cm_dsp_id=18&expiration=1804360533&external_user_id=0b0c8932-2b37-4189-9b34-60bc2925fbf4
Request Chain 443
  • https://gw-iad-bid.ymmobi.com/adx/user/sync?pubid=aW5kZXhleGNoYW5nZQ==&gdpr=&gdpr_consent=&us_privacy=&callback=https%3A%2F%2Fdsum-sec.casalemedia.com%2Fcrum%3Fcm_dsp_id%3D259%26external_user_id%3D%7Bym_user_id%7D%26gdpr%3D%7BGDPR%7D%26gdpr_consent%3D%7BGDPR_CONSENT%7D%26us_privacy%3D%7BUS_PRIVACY%7D HTTP 302
  • https://dsum-sec.casalemedia.com/crum?cm_dsp_id=259&external_user_id=ym_user_439cbae0-731d-48fe-9587-4aa98bfc5796&gdpr=&gdpr_consent=&us_privacy=
Request Chain 444
  • https://cm.ctnsnet.com/int/cm?exc=19 HTTP 302
  • https://dsum-sec.casalemedia.com/crum?cm_dsp_id=109&external_user_id=f77350423da8456c84c50f5934fdc8e4&expiration=1791314133
Request Chain 483
  • https://pixel-us-east.rubiconproject.com/exchange/sync.php?p=16698&gdpr=0&us_privacy=1NN-&gdpr=0&us_privacy=1NN-&khaos=MTQ6Z31F-16-DHLJ HTTP 302
  • https://sync.taboola.com/sg/rubiconvideo-network/1/rtb-h/?taboola_hm=MTQ6Z31F-16-DHLJ&gdpr=0&us_privacy=1NN-
Request Chain 490
  • https://cm.g.doubleclick.net/pixel?google_nid=rubicon&google_cm&google_sc&process_consent=T&gdpr=0&us_privacy=1NN- HTTP 302
  • https://pixel.rubiconproject.com/tap.php?v=7751&nid=2249&expires=30&gdpr=0&put=CAESEGTooumNkdT5OS2kPtkpnTE&google_cver=1
Request Chain 491
  • https://token.rubiconproject.com/token?pid=2249&pt=n&gdpr=0&us_privacy=1NN- HTTP 302
  • https://cm.g.doubleclick.net/pixel?google_nid=rubicon&google_hm=YmJlOTBlOGY1ODY3ZmFjMDc5YTA0OTlhMmNiNzRhZjViZGNhNjNlMA&gdpr=0&us_privacy=1NN-
Request Chain 492
  • https://s.amazon-adsystem.com/dcm?pid=50cd21b7-d8d7-4615-9fb9-a2be831f8488&id=&gdpr=0&us_privacy=1NN- HTTP 302
  • https://s.amazon-adsystem.com/dcm?pid=50cd21b7-d8d7-4615-9fb9-a2be831f8488&id=&gdpr=0&us_privacy=1NN-&dcc=t
Request Chain 493
  • https://match.adsrvr.org/track/cmf/rubicon?gdpr=0&us_privacy=1NN- HTTP 302
  • https://pixel.rubiconproject.com/tap.php?v=8981&nid=2307&put=854f06c6-0e88-4afd-a936-6a879ff410f4&gdpr=0&gdpr_consent=&expires=30
Request Chain 494
  • https://token.rubiconproject.com/token?pid=2974&pt=n&a=1&gdpr=0&us_privacy=1NN- HTTP 302
  • https://ups.analytics.yahoo.com/ups/58912/cms?uid=hGVu7F95kI0ZWBPZuCf16Mn5EUdSAgOZEtemQ7w0kco&csrc=&gdpr=0&us_privacy=1NN-
Request Chain 495
  • https://token.rubiconproject.com/token?pid=25470&gdpr=0&us_privacy=1NN- HTTP 302
  • https://cm.g.doubleclick.net/pixel?google_nid=rp&google_cm&google_hm=TVRRNlozMUYtMTYtREhMSg==&gdpr=0&us_privacy=1NN- HTTP 302
  • https://pixel.rubiconproject.com/exchange/sync.php?p=dfp&gdpr=0&google_gid=CAESEI7avJGeVkZ7m0ANB9n2Tq0&google_cver=1 HTTP 302
  • https://cm.g.doubleclick.net/pixel?google_nid=rp&google_hm=TVRRNlozNFotSi04QkJP&google_push=&gdpr=0
Request Chain 497
  • https://pixel.rubiconproject.com/exchange/sync.php?p=a9us&gdpr=0&us_privacy=1NN- HTTP 302
  • https://s.amazon-adsystem.com/ecm3?id=MTQ6Z31F-16-DHLJ&ex=d-rubiconproject.com&status=ok&gdpr=0&us_privacy=1NN-
Request Chain 498
  • https://aax-eu.amazon-adsystem.com/s/dcm?pid=a38a8ddf-19a7-4ab8-ba05-0a61de92a7e5&id=&gdpr=0&us_privacy=1NN- HTTP 302
  • https://aax-eu.amazon-adsystem.com/s/dcm?pid=a38a8ddf-19a7-4ab8-ba05-0a61de92a7e5&id=&gdpr=0&us_privacy=1NN-&dcc=t
Request Chain 499
  • https://token.rubiconproject.com/token?pid=36584&gdpr=0&us_privacy=1NN- HTTP 302
  • https://px.ads.linkedin.com/setuid?partner=rubiconDb&dbredirect=true&ruxId=MTQ6Z31F-16-DHLJ&gdpr=0&us_privacy=1NN-
Request Chain 500
  • https://match.prod.bidr.io/cookie-sync/rp?bee_sync_partners=rp&gdpr=0&us_privacy=1NN- HTTP 303
  • https://match.prod.bidr.io/cookie-sync/rp?bee_sync_partners=rp&gdpr=0&us_privacy=1NN-&_bee_ppp=1 HTTP 303
  • https://pixel.rubiconproject.com/tap.php?v=183462&nid=4114&put=AADYKE7VO3gAAAEE4bjSQA&expires=30&gdpr=0
Request Chain 501
  • https://pixel.rubiconproject.com/exchange/sync.php?p=pbs-adaptmx&gdpr=0&us_privacy=1NN- HTTP 302
  • https://sync.a-mo.net/setuid/magnite?uid=MTQ6Z34Z-J-8BBO&gdpr=0&us_privacy=1NN-
Request Chain 502
  • https://sync.ipredictive.com/d/sync/cookie/generic?https://pixel.rubiconproject.com/tap.php?v=17149&nid=2861&put=${ADELPHIC_CUID}&expires=30&gdpr=0&us_privacy=1NN- HTTP 302
  • https://pixel.rubiconproject.com/tap.php?v=17149&nid=2861&put=c2269529-3548-4f51-8d0e-282d6628d5d4&expires=30&gdpr=0&us_privacy=1NN-
Request Chain 503
  • https://pixel.rubiconproject.com/exchange/sync.php?p=pbs-apn&gdpr=0&us_privacy=1NN- HTTP 302
  • https://ib.adnxs.com/prebid/setuid?bidder=rubicon&uid=MTQ6Z34Z-J-8BBO&gdpr=0&us_privacy=1NN-
Request Chain 504
  • https://pixel.rubiconproject.com/exchange/sync.php?p=19564&gdpr=0&us_privacy=1NN- HTTP 302
  • https://capi.connatix.com/us/pixel?puid=MTQ6Z34Z-J-8BBO&pId=11&gdpr=&gdpr_consent=&us_privacy=&gdpr=0&us_privacy=1NN-
Request Chain 505
  • https://token.rubiconproject.com/token?pid=37556&a=1&gdpr=0&us_privacy=1NN- HTTP 302
  • https://pixel.tapad.com/idsync/ex/receive?partner_id=3355&partner_device_id=MTQ6Z34Z-J-8BBO&gdpr=0&us_privacy=1NN- HTTP 302
  • https://pixel.tapad.com/idsync/ex/receive/check?partner_id=3355&partner_device_id=MTQ6Z34Z-J-8BBO&gdpr=0&us_privacy=1NN-
Request Chain 509
  • https://pixel-us-east.rubiconproject.com/exchange/sync.php?p=16698&gdpr=0&us_privacy=1NN-&gdpr=0&us_privacy=1NN-&khaos=MTQ6Z34Z-J-8BBO HTTP 302
  • https://sync.taboola.com/sg/rubiconvideo-network/1/rtb-h/?taboola_hm=MTQ6Z34Z-J-8BBO&gdpr=0&us_privacy=1NN-
Request Chain 634
  • https://image8.pubmatic.com/AdServer/ImgSync?p=156307&gdpr=gdpr=0&&gdpr_consent=&pu=https%3A%2F%2Fimage4.pubmatic.com%2FAdServer%2FSPug%3Fp%3D156307%26mpc%3D4%26fp%3D1%26pmc%3DPM_PMC%26pr%3Dhttps%253A%252F%252Fsync.taboola.com%252Fsg%252Frtb-pubmatic-network%252F1%252Frtb-h%253Ftaboola_hm%253D%2523PMUID HTTP 302
  • https://image8.pubmatic.com/AdServer/ImgSync?p=156307&gdpr=gdpr=0&&gdpr_consent=&pu=https%3A%2F%2Fimage4.pubmatic.com%2FAdServer%2FSPug%3Fp%3D156307%26mpc%3D4%26fp%3D1%26pmc%3DPM_PMC%26pr%3Dhttps%253A%252F%252Fsync.taboola.com%252Fsg%252Frtb-pubmatic-network%252F1%252Frtb-h%253Ftaboola_hm%253D%2523PMUID&rdf=1 HTTP 302
  • https://cm.g.doubleclick.net/pixel?google_nid=pubmatic&google_hm=OEMyRUFENEYtQTQ1Ni00NDRBLThFOUEtNjM4RDgxOTc0RDkx&gdpr=-1&gdpr_consent=&google_cm HTTP 302
  • https://image2.pubmatic.com/AdServer/Pug?vcode=bz0yJnR5cGU9MSZjb2RlPTIxNzcmdGw9MTI5NjAw&gdpr=-1&gdpr_consent=&piggybackCookie=CAESEAPqTl9B4XpoO-jMg8QyV8s&google_cver=1 HTTP 302
  • https://image8.pubmatic.com/AdServer/ImgSync?sec=1&gdpr=0&gdpr_consent=&us_privacy= HTTP 302
  • https://image4.pubmatic.com/AdServer/SPug?fp=1&gdpr=0&mpc=4&p=156307&pmc=1&pr=https%3A%2F%2Fsync.taboola.com%2Fsg%2Frtb-pubmatic-network%2F1%2Frtb-h%3Ftaboola_hm%3D15934B2C-AE30-4515-9CE0-02BC4EDC0B5E HTTP 302
  • https://sync.taboola.com/sg/rtb-pubmatic-network/1/rtb-h?taboola_hm=15934B2C-AE30-4515-9CE0-02BC4EDC0B5E
Request Chain 636
  • https://creativecdn.com/cm-notify?pi=taboola HTTP 302
  • https://sync.taboola.com/sg/rtbhouse-network/1/rtb-h?taboola_hm=rhvrGoZzJvZi2sQgRiU87MebV0cruRe4rSwCGZyXCtY&pi=taboola
Request Chain 648
  • https://image8.pubmatic.com/AdServer/ImgSync?p=156307&gdpr=gdpr=0&&gdpr_consent=&pu=https%3A%2F%2Fimage4.pubmatic.com%2FAdServer%2FSPug%3Fp%3D156307%26mpc%3D4%26fp%3D1%26pmc%3DPM_PMC%26pr%3Dhttps%253A%252F%252Fsync.taboola.com%252Fsg%252Frtb-pubmatic-network%252F1%252Frtb-h%253Ftaboola_hm%253D%2523PMUID HTTP 302
  • https://image8.pubmatic.com/AdServer/ImgSync?p=156307&gdpr=gdpr=0&&gdpr_consent=&pu=https%3A%2F%2Fimage4.pubmatic.com%2FAdServer%2FSPug%3Fp%3D156307%26mpc%3D4%26fp%3D1%26pmc%3DPM_PMC%26pr%3Dhttps%253A%252F%252Fsync.taboola.com%252Fsg%252Frtb-pubmatic-network%252F1%252Frtb-h%253Ftaboola_hm%253D%2523PMUID&rdf=1 HTTP 302
  • https://cm.g.doubleclick.net/pixel?google_nid=pubmatic&google_hm=MTU5MzRCMkMtQUUzMC00NTE1LTlDRTAtMDJCQzRFREMwQjVF&gdpr=-1&gdpr_consent=&google_cm HTTP 302
  • https://image2.pubmatic.com/AdServer/Pug?vcode=bz0yJnR5cGU9MSZjb2RlPTIxNzcmdGw9MTI5NjAw&gdpr=-1&gdpr_consent=&piggybackCookie=CAESEAPqTl9B4XpoO-jMg8QyV8s&google_cver=1 HTTP 302
  • https://image8.pubmatic.com/AdServer/ImgSync?sec=1&gdpr=0&gdpr_consent=&us_privacy= HTTP 302
  • https://cm.g.doubleclick.net/pixel?google_nid=pubmatic&google_cm&google_sc&gdpr=0&gdpr_consent= HTTP 302
  • https://image2.pubmatic.com/AdServer/Pug?vcode=bz0yJnR5cGU9MSZjb2RlPTIxNzcmdGw9MTI5NjAw&gdpr=0&gdpr_consent=&piggybackCookie=CAESEAPqTl9B4XpoO-jMg8QyV8s&google_cver=1 HTTP 302
  • https://image8.pubmatic.com/AdServer/ImgSync?sec=1&gdpr=0&gdpr_consent=&us_privacy= HTTP 302
  • https://match.adsrvr.org/track/cmf/generic?ttd_pid=pubmatic&ttd_tpi=1&gdpr=0&gdpr_consent= HTTP 302
  • https://simage2.pubmatic.com/AdServer/Pug?vcode=bz0yJnR5cGU9MSZjb2RlPTI4NDkmdGw9MTI5NjAw&piggybackCookie=854f06c6-0e88-4afd-a936-6a879ff410f4&gdpr=0&gdpr_consent= HTTP 302
  • https://image8.pubmatic.com/AdServer/ImgSync?sec=1&gdpr=0&gdpr_consent=&us_privacy=
Request Chain 650
  • https://creativecdn.com/cm-notify?pi=taboola HTTP 302
  • https://sync.taboola.com/sg/rtbhouse-network/1/rtb-h?taboola_hm=rhvrGoZzJvZi2sQgRiU87MebV0cruRe4rSwCGZyXCtY&pi=taboola
Request Chain 664
  • https://match.prod.bidr.io/cookie-sync/ie HTTP 303
  • https://dsum-sec.casalemedia.com/crum?cm_dsp_id=130&external_user_id=AADYKE7VO3gAAAEE4bjSQA&expiration=1789931737
Request Chain 665
  • https://trace.mediago.io/ju/cs/indexexchange?gdpr=&gdpr_consent=&us_privacy=&gpp=&gpp_sid= HTTP 302
  • https://dsum-sec.casalemedia.com/crum?cm_dsp_id=215&external_user_id=2fa06cb2d07f2c2525scgp00mtq6z70i
Request Chain 666
  • https://c1.adform.net/serving/cookie/match?party=29 HTTP 302
  • https://dsum-sec.casalemedia.com/crum?cm_dsp_id=111&external_user_id=4965478313182929533&expiration=1789931737
Request Chain 667
  • https://x.bidswitch.net/sync?ssp=index HTTP 302
  • https://x.bidswitch.net/ul_cb/sync?ssp=index HTTP 302
  • https://p.rfihub.com/cm?in=1&pub=20513&ssp=index&gdpr=&gdpr_consent= HTTP 302
  • https://x.bidswitch.net/sync?dsp_id=119&user_id=5109685644081392132&expires=30&gdpr=&gdpr_consent=&ssp=index HTTP 302
  • https://dsum.casalemedia.com/rum?cm_dsp_id=51&external_user_id=2de07641-a72b-4989-9e69-99a66f1c539a&gdpr=&gdpr_consent=&us_privacy=
Request Chain 668
  • https://sync-tm.everesttech.net/upi/pid/ZMAwryCI?redir=https%3A%2F%2Fdsum-sec.casalemedia.com%2Frum%3Fcm_dsp_id%3D88%26external_user_id%3D%24%7BTM_USER_ID%7D HTTP 302
  • https://sync-tm.everesttech.net/ct/upi/pid/ZMAwryCI?redir=https%3A%2F%2Fdsum-sec.casalemedia.com%2Frum%3Fcm_dsp_id%3D88%26external_user_id%3D%24%7BTM_USER_ID%7D&_test=ap272QAAAG5GjwBD
Request Chain 669
  • https://d.adroll.com/cm/index/tp_out?advertisable=3GMDZMBFQREVBC75SYYKWH HTTP 302
  • https://dsum-sec.casalemedia.com/crum?cm_dsp_id=105&external_user_id=MWRlYmRjNTFmYzExYTVhYTZhOTMzYWRmMmIzYmZlYjk&expiration=1820258137
Request Chain 670
  • https://pixel-sync.sitescout.com/dmp/pixelSync?nid=48 HTTP 302
  • https://pixel-sync.sitescout.com/dmp/pixelSync?cookieQ=1&nid=48 HTTP 302
  • https://pixel.tapad.com/idsync/ex/push?partner_id=2499&partner_device_id=ac437ca2-c7bb-4dc5-b5b7-78fab6b24a19-6a9dbbd9-494c&partner_url=https%3A%2F%2Fdsum-sec.casalemedia.com%2Fcrum%3Fcm_dsp_id%3D64%26external_user_id%3Dac437ca2-c7bb-4dc5-b5b7-78fab6b24a19-6a9dbbd9-494c%26gdpr%3D0%26gdpr_consent%3D%26gpp%3D%26gpp_sid%3D HTTP 302
  • https://dsum-sec.casalemedia.com/crum?cm_dsp_id=64&external_user_id=ac437ca2-c7bb-4dc5-b5b7-78fab6b24a19-6a9dbbd9-494c&gdpr=0&gdpr_consent=&gpp=&gpp_sid=

667 HTTP transactions Go Pro

Only in urlscan Pro

Inspect WebSocket connections, examine POST data effortlessly, and track overlap counts in real time. Features live search and filtering across all HTTP output, complete with full response metadata for deep analysis.
Click for more information
Free trials of urlscan Pro are available.

20 data transactions

Method
Protocol
Status Resource
Path
Size
x-fer
Time
Latency
Type
MIME-Type
IP
Location
GET
H2
200
Primary Request / Show response
abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
327 KB
66 KB
592ms
334ms
Document
text/html
18.65.39.76
Amazon.com
General
Full URL
https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
18.65.39.76 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-18-65-39-76.ams1.r.cloudfront.net
Software
nginx /
Resource Hash
d8640335d4607873418c1ceb9844719dd1b20f071574dd34523f4989ef86effc

Request headers

Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

cache-control
max-age=6
content-encoding
gzip
content-type
text/html; charset=utf-8
date
Sun, 06 Sep 2026 19:15:26 GMT
expires
Sun, 06 Sep 2026 19:15:32 GMT
last-modified
Sun, 06 Sep 2026 19:15:32 GMT
server
nginx
vary
Accept-Encoding
via
1.1 045d55468661252b6be78e701e36b492.cloudfront.net (CloudFront)
x-amz-cf-id
gdLX2FmDfWMYPXYcDbuoGDLAiCY5k_oyynVCdbr_7tIbewSnVZKnsw==
x-amz-cf-pop
AMS1-P1
x-cache
Miss from cloudfront
GET
H2
200
fusion-75eda2ba.css
assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/css/
416 KB
92 KB
338ms
109ms
Stylesheet
text/css
13.32.121.29
Amazon.com
General
Full URL
https://assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/css/fusion-75eda2ba.css
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.29 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-29.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
f9d44167d8f6caa16c25ce7873b2e0a4403f66b88d3df7bcbb8cfb912275d149

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
gzip
etag
W/"d66e012ed062e1f40fbf72ae335cce6d"
age
358945
via
1.1 24ba6ae31527 (Varnish/7.5), 1.1 06a27d66e25d02ebcfb014b9d194016a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
content-length
94005
x-amz-cf-id
BJTCqK_5Ag3ywfjFAtY2N6_WNTfn5t9g5nDiltb-X9lr2DsqCgc16Q==
date
Wed, 02 Sep 2026 15:33:01 GMT
content-type
text/css
last-modified
Wed, 02 Sep 2026 01:36:34 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
GET
H2
200
6160-4b6b3f4a.css
assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/css/
25 KB
6 KB
347ms
119ms
Stylesheet
text/css
13.32.121.29
Amazon.com
General
Full URL
https://assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/css/6160-4b6b3f4a.css
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.29 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-29.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
6514f8837175083bcd32c8ffd78e0a419307e72ded731f34f8773d48344334c1

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
gzip
etag
W/"5eef42b46754453ee6b0cef8d433b75d"
age
358980
via
1.1 56e755a34cf9 (Varnish/7.5), 1.1 06a27d66e25d02ebcfb014b9d194016a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
content-length
6228
x-amz-cf-id
VmiC3odSFbniH4muqSIr-apCMFWgBalyfDvCVyMEi_Zl0yeV_nDD9A==
date
Wed, 02 Sep 2026 15:32:26 GMT
content-type
text/css
last-modified
Wed, 02 Sep 2026 01:36:34 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
GET
H2
200
abcotv-149cfe50.css
assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/css/
15 KB
4 KB
485ms
256ms
Stylesheet
text/css
13.32.121.29
Amazon.com
General
Full URL
https://assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/css/abcotv-149cfe50.css
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.29 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-29.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
68094cc2993c91884079842eb15892006395f2d47a8b029a791be03dbe2138c3

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
gzip
etag
W/"b77782c762ef2c68c814cd5b90f84d7a"
age
358170
via
1.1 24ba6ae31527 (Varnish/7.5), 1.1 06a27d66e25d02ebcfb014b9d194016a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
content-length
3817
x-amz-cf-id
8ovhag5-tcEWeql3q-Nua0CbEdJZ5AAYD6H_NswPsVutmEsm1CYAtw==
date
Wed, 02 Sep 2026 15:45:56 GMT
content-type
text/css
last-modified
Wed, 02 Sep 2026 01:36:34 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
GET
H2
200
9249-8cc41c27.css
assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/css/
17 KB
4 KB
493ms
265ms
Stylesheet
text/css
13.32.121.29
Amazon.com
General
Full URL
https://assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/css/9249-8cc41c27.css
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.29 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-29.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
a0caa36461d8f37cb9ae711cf57ecba12e5f848ee24d9943dbb90fd73dec9bc4

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
gzip
etag
W/"1678b1b6314e15137aa04dcd7c6f292f"
age
358979
via
1.1 c2856877bfae (Varnish/7.5), 1.1 06a27d66e25d02ebcfb014b9d194016a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
content-length
3623
x-amz-cf-id
wkgzgo2LA7WqSaawBZrVwd_zKwKrtp-q4iulgU8gOLa2hjcYtUmr2g==
date
Wed, 02 Sep 2026 15:32:27 GMT
content-type
text/css
last-modified
Wed, 02 Sep 2026 01:36:34 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
vary
Accept-Encoding
GET
H2
200
9524-f3cede7b.css
assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/css/
21 KB
4 KB
489ms
261ms
Stylesheet
text/css
13.32.121.29
Amazon.com
General
Full URL
https://assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/css/9524-f3cede7b.css
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.29 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-29.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
f31277b57344b9e570f4a8d6f4c092988ad6d292909144919af9f31df54e1c3f

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
gzip
etag
W/"ca37b43f61515cd26b2e4b74f1ea8c9f"
age
358980
via
1.1 24ba6ae31527 (Varnish/7.5), 1.1 06a27d66e25d02ebcfb014b9d194016a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
content-length
4078
x-amz-cf-id
LVtXNHBqJQEX0uvsYEJLvTnwxEoBU9dbktjUHPo-J46gU3abCzZb7g==
date
Wed, 02 Sep 2026 15:32:26 GMT
content-type
text/css
last-modified
Wed, 02 Sep 2026 01:36:34 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
vary
Accept-Encoding
GET
H2
200
prism-story-f4c05870.css
assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/css/
4 KB
2 KB
486ms
259ms
Stylesheet
text/css
13.32.121.29
Amazon.com
General
Full URL
https://assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/css/prism-story-f4c05870.css
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.29 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-29.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
e1e1290ea557602cc7a320cba08978fab0c9b2e5e5a1846a9aa3b81c52eb0ec4

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
gzip
etag
W/"a2bb90d963f6814b7dd09b46963ce4bc"
age
358980
via
1.1 24ba6ae31527 (Varnish/7.5), 1.1 06a27d66e25d02ebcfb014b9d194016a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
content-length
1163
x-amz-cf-id
Pojss5Xsz3qtIlrWH-erA_w6_WNNhodGcQtZh3aY_s96Zd4Q02_qvg==
date
Wed, 02 Sep 2026 15:32:26 GMT
content-type
text/css
last-modified
Wed, 02 Sep 2026 01:36:34 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
vary
Accept-Encoding
GET
H2
200
Bootstrap.js Show response
dcf.espn.com/TWDC-DTCI/prod/
668 KB
122 KB
458ms
175ms
Script
application/javascript
3.124.173.63
Amazon.com
General
Full URL
https://dcf.espn.com/TWDC-DTCI/prod/Bootstrap.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
3.124.173.63 Frankfurt am Main, Germany, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-3-124-173-63.eu-central-1.compute.amazonaws.com
Software
CloudFront /
Resource Hash
0c9fea29a6c58114fa4a58890357aa1b03797c57f8bce522a034181948f476eb

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
x-amz-version-id
a2supBKhsQ0lew.I1ODFA1swjHJaalc7
etag
W/"4882d4f2ba0bd0a6a184d3eb12da66ac"
age
265344
alt-svc
h3=":443"; ma=86400
x-cache
Hit from cloudfront
x-amz-cf-id
gU17mA8aBmhEMF6TCaiXYzTdUjlxhIcX0sJFFr5iTf9MPqa6KFwiWA==
date
Sun, 06 Sep 2026 19:15:26 GMT
content-type
application/javascript; charset=utf-8
vary
Accept-Encoding, Origin
last-modified
Thu, 03 Sep 2026 17:32:18 GMT
x-amz-replication-status
COMPLETED
cache-control
max-age=300
via
1.1 fa87f2173bfe5d35fd73cec71ab12a32.cloudfront.net (CloudFront)
x-amz-cf-pop
FRA56-P7
server
CloudFront
x-amz-server-side-encryption
AES256
GET
H2
200
PostGrotesk-Book.woff2
s.abcnews.com/assets/dtci/fonts/post-grotesk/
51 KB
52 KB
392ms
135ms
Font
application/octet-stream
13.32.121.2
Amazon.com
General
Full URL
https://s.abcnews.com/assets/dtci/fonts/post-grotesk/PostGrotesk-Book.woff2
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.2 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-2.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
19f51b9f3812c72be9330c350365819a1915a49c83fc70a94216ae154255651d

Request headers

Origin
https://abc7.com
sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
3000
x-amz-version-id
null
etag
"6f0942a878183d0b7c862df9487eb857"
age
581
access-control-allow-methods
GET
x-amz-meta-user-agent-id
abcnewssite@s-0da66bcd175040bb8
x-cache
Hit from cloudfront
x-amz-cf-id
p360t3NrT0sn_tXu-htJkwevMzApzL9CmXvfVODphn09Yc6vGJ-jBA==
date
Sun, 06 Sep 2026 19:05:52 GMT
content-type
application/octet-stream
last-modified
Mon, 23 Mar 2020 15:13:08 GMT
x-amz-meta-user-agent
AWSTransfer
vary
Origin,Access-Control-Request-Headers,Access-Control-Request-Method,Accept-Encoding
via
1.1 5fa65194b963365c20fbd28444032cfc.cloudfront.net (CloudFront)
accept-ranges
bytes
access-control-allow-origin
*
content-length
52408
x-amz-cf-pop
FRA60-P1
server
AmazonS3
GET
H2
200
PostGrotesk-Bold.woff2
s.abcnews.com/assets/dtci/fonts/post-grotesk/
52 KB
53 KB
391ms
133ms
Font
application/octet-stream
13.32.121.2
Amazon.com
General
Full URL
https://s.abcnews.com/assets/dtci/fonts/post-grotesk/PostGrotesk-Bold.woff2
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.2 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-2.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
1e49123b4fbb3d1cdd7b9d5500ca1c342dfc9ca17c3d5abf9f0116b21acfa803

Request headers

Origin
https://abc7.com
sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
3000
x-amz-version-id
null
etag
"d2b1c24d4a273a948721aada03d20341"
age
745
access-control-allow-methods
GET
x-amz-meta-user-agent-id
abcnewssite@s-0da66bcd175040bb8
x-cache
Hit from cloudfront
x-amz-cf-id
9TQUiQWw5ZoVZ_XzDnJuPezR3a2N6TCAvVtGkIy2W3BJKETgoOkQKg==
date
Sun, 06 Sep 2026 19:03:16 GMT
content-type
application/octet-stream
last-modified
Mon, 23 Mar 2020 15:13:07 GMT
x-amz-meta-user-agent
AWSTransfer
vary
Origin,Access-Control-Request-Headers,Access-Control-Request-Method,Accept-Encoding
via
1.1 5fa65194b963365c20fbd28444032cfc.cloudfront.net (CloudFront)
accept-ranges
bytes
access-control-allow-origin
*
content-length
53436
x-amz-cf-pop
FRA60-P1
server
AmazonS3
GET
H2
200
PostGrotesk-Medium.woff2
s.abcnews.com/assets/dtci/fonts/post-grotesk/
53 KB
54 KB
390ms
133ms
Font
application/octet-stream
13.32.121.2
Amazon.com
General
Full URL
https://s.abcnews.com/assets/dtci/fonts/post-grotesk/PostGrotesk-Medium.woff2
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.2 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-2.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
24a468038d47f4650998a26a4c9dd35628ba0b8d4cf7a05ea5c9779462662b5b

Request headers

Origin
https://abc7.com
sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
3000
x-amz-version-id
null
etag
"42993872498ed6f7da1c44bf965ce41d"
age
1513
access-control-allow-methods
GET
x-amz-meta-user-agent-id
abcnewssite@s-0da66bcd175040bb8
x-cache
Hit from cloudfront
x-amz-cf-id
8Y9cLvZ-phb9VoXQTXv8poEu_2D8L3ZV1qWhAHTVGMi8GAzvUCdfRQ==
date
Sun, 06 Sep 2026 18:50:32 GMT
content-type
application/octet-stream
last-modified
Mon, 23 Mar 2020 15:13:10 GMT
x-amz-meta-user-agent
AWSTransfer
vary
Origin,Access-Control-Request-Headers,Access-Control-Request-Method,Accept-Encoding
via
1.1 5fa65194b963365c20fbd28444032cfc.cloudfront.net (CloudFront)
accept-ranges
bytes
access-control-allow-origin
*
content-length
54416
x-amz-cf-pop
FRA60-P1
server
AmazonS3
GET
H2
200
TiemposText-Regular.woff2
s.abcnews.com/assets/dtci/fonts/klim/tiempos/
49 KB
49 KB
391ms
134ms
Font
application/octet-stream
13.32.121.2
Amazon.com
General
Full URL
https://s.abcnews.com/assets/dtci/fonts/klim/tiempos/TiemposText-Regular.woff2
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.2 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-2.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
f4e3881d17cf551a4ef101f1b98d44ea9b4e43018bd45751bdae718e4f8866ba

Request headers

Origin
https://abc7.com
sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
3000
x-amz-version-id
null
etag
"cad633c7e5471196d61ae4ab0159b0d9"
age
260
access-control-allow-methods
GET
x-amz-meta-user-agent-id
abcnewssite@s-0da66bcd175040bb8
x-cache
Hit from cloudfront
x-amz-cf-id
0c7smXN7TA3mnbb3fXbCMZBzfIkT4LJ-TCYM-NoWnboTHEdpmua3IQ==
date
Sun, 06 Sep 2026 19:12:30 GMT
content-type
application/octet-stream
last-modified
Fri, 11 Oct 2019 19:31:02 GMT
x-amz-meta-user-agent
AWSTransfer
vary
Origin,Access-Control-Request-Headers,Access-Control-Request-Method,Accept-Encoding
via
1.1 5fa65194b963365c20fbd28444032cfc.cloudfront.net (CloudFront)
accept-ranges
bytes
access-control-allow-origin
*
content-length
49910
x-amz-cf-pop
FRA60-P1
server
AmazonS3
GET
H2
200
runtime-78295c40.js Show response
assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/
4 KB
2 KB
108ms
108ms
Script
application/javascript
13.32.121.29
Amazon.com
General
Full URL
https://assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/runtime-78295c40.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.29 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-29.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
0b2c33a3a284f7ad1ac57da0edb3682d98eaa9927f9d5829c8d1102a409fde0c

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
br
etag
W/"7fc17e59562215bd6fbc93df34cf2493"
age
358170
via
1.1 24ba6ae31527 (Varnish/7.5), 1.1 06a27d66e25d02ebcfb014b9d194016a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
x-amz-cf-id
ZqqsVLbjs0pcsc7fybYnY5J_-JviqFP6BefJmRtmDDZqO4XaHpg6Sg==
date
Wed, 02 Sep 2026 15:45:56 GMT
content-type
application/javascript
last-modified
Wed, 02 Sep 2026 01:36:35 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
vary
Accept-Encoding
GET
H2
200
6160-88d3eb3f.js Show response
assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/
3 MB
758 KB
109ms
109ms
Script
application/javascript
13.32.121.29
Amazon.com
General
Full URL
https://assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/6160-88d3eb3f.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.29 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-29.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
f4d06ced36abbd090d811c727eda65dd3166332741d0b2e1b8de355bf14d50cd

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
gzip
etag
W/"3b63decbd004af7ce539bc84a655325e"
age
358973
via
1.1 24ba6ae31527 (Varnish/7.5), 1.1 06a27d66e25d02ebcfb014b9d194016a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
x-amz-cf-id
g22Rk-pP0BlbAjs3DTLXTSHlMJZavFCPp6J4JeIgJvDewbMGdPUwaA==
date
Wed, 02 Sep 2026 15:32:33 GMT
content-type
application/javascript
last-modified
Wed, 02 Sep 2026 01:36:34 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
vary
Accept-Encoding
GET
H2
200
507-639103b4.js Show response
assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/
11 KB
4 KB
244ms
240ms
Script
application/javascript
13.32.121.29
Amazon.com
General
Full URL
https://assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/507-639103b4.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.29 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-29.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
4054a923594915a2c73a3067f34d26d66d3668819043969dd124af040f4d06b1

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
gzip
etag
W/"9e7ada9e2390971b9b2c40ddc8d92392"
age
358942
via
1.1 56e755a34cf9 (Varnish/7.5), 1.1 06a27d66e25d02ebcfb014b9d194016a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
x-amz-cf-id
qJPabGPYhi1WH_BqxeZHcUW5-7Qp_AdLJ9raS-dpssPtPm7B8ZNXxQ==
date
Wed, 02 Sep 2026 15:33:05 GMT
content-type
application/javascript
last-modified
Wed, 02 Sep 2026 01:36:34 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
vary
Accept-Encoding
GET
H2
200
2489-51ad799d.js Show response
assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/
2 MB
431 KB
247ms
243ms
Script
application/javascript
13.32.121.29
Amazon.com
General
Full URL
https://assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/2489-51ad799d.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.29 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-29.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
51d1d7da9e3bd1029112fee3dc79c3b12980311fea5ef05a8994687c817cf9e7

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
gzip
etag
W/"acacc7acec853358d101cc57b6e6cf1d"
age
358974
via
1.1 56e755a34cf9 (Varnish/7.5), 1.1 06a27d66e25d02ebcfb014b9d194016a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
x-amz-cf-id
pxMZNzD2ohggZUqTWsLgL-rotMuvZUtJhKJwxEDtEG6FCZXbAE5RZg==
date
Wed, 02 Sep 2026 15:32:33 GMT
content-type
application/javascript
last-modified
Wed, 02 Sep 2026 01:36:34 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
vary
Accept-Encoding
GET
H2
200
2561-2bebf93f.js Show response
assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/
6 KB
3 KB
244ms
241ms
Script
application/javascript
13.32.121.29
Amazon.com
General
Full URL
https://assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/2561-2bebf93f.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.29 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-29.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
a6b0daa08bb479dc4349a51b2bf8d3340a45e3c5a651b4d69450d3f8eae4870c

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
br
etag
W/"542aeb8953879b4037ea9ecdbd2ac36a"
age
358170
via
1.1 56e755a34cf9 (Varnish/7.5), 1.1 06a27d66e25d02ebcfb014b9d194016a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
x-amz-cf-id
u2yH4UIdaC5ybhYDKouQjn2-hRPaxN42_QawPla5exbl4S5s4iEv2g==
date
Wed, 02 Sep 2026 15:45:57 GMT
content-type
application/javascript
last-modified
Wed, 02 Sep 2026 01:36:34 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
vary
Accept-Encoding
GET
H2
200
9249-4886474c.js Show response
assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/
1 MB
135 KB
245ms
241ms
Script
application/javascript
13.32.121.29
Amazon.com
General
Full URL
https://assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/9249-4886474c.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.29 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-29.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
54dddfa0f7704dad85c3523b51f38b6f627786dbf876bef069f22fcde8ada69e

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
br
etag
W/"676dcff75119f59b085e621d0c6d26bc"
age
358170
via
1.1 c2856877bfae (Varnish/7.5), 1.1 06a27d66e25d02ebcfb014b9d194016a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
x-amz-cf-id
FgXWZzYyW3finbBjIyImenqmnbpmMTMr0sA2MA-03s4VOYtIvS6pDg==
date
Wed, 02 Sep 2026 15:45:57 GMT
content-type
application/javascript
last-modified
Wed, 02 Sep 2026 01:36:34 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
vary
Accept-Encoding
GET
H2
200
7090-2eb94ea1.js Show response
assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/
25 KB
10 KB
246ms
242ms
Script
application/javascript
13.32.121.29
Amazon.com
General
Full URL
https://assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/7090-2eb94ea1.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.29 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-29.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
a474be388ddc2a82941a93c948de692ac0385121c4ef9a74276fe684082fe512

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
gzip
etag
W/"62454a4ed7f93d3ebb001ee5bf2db157"
age
358974
via
1.1 56e755a34cf9 (Varnish/7.5), 1.1 06a27d66e25d02ebcfb014b9d194016a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
x-amz-cf-id
YzDeHYhu_eJp6i_wp5GCbk0kmOJWl6CRLDFT7ZZPShVpuvfzbvs03w==
date
Wed, 02 Sep 2026 15:32:33 GMT
content-type
application/javascript
last-modified
Wed, 02 Sep 2026 01:36:34 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
vary
Accept-Encoding
GET
H2
200
4340-d1b21268.js Show response
assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/
614 KB
183 KB
247ms
243ms
Script
application/javascript
13.32.121.29
Amazon.com
General
Full URL
https://assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/4340-d1b21268.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.29 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-29.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
33bae0bb5256e520f717cff39be6980efc3ddb22a3356a76ca117c8ebd0034cd

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
gzip
etag
W/"cec4c2b9ed6b609b06b73cfcbd0643d8"
age
358974
via
1.1 24ba6ae31527 (Varnish/7.5), 1.1 06a27d66e25d02ebcfb014b9d194016a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
x-amz-cf-id
7nYftXO92lXuy7fbKotD7kxvVBIyvQggFdWnjzHT8xrMr1KsLSXK-A==
date
Wed, 02 Sep 2026 15:32:33 GMT
content-type
application/javascript
last-modified
Wed, 02 Sep 2026 01:36:34 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
vary
Accept-Encoding
GET
H2
200
1837-34eb9da4.js Show response
assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/
12 KB
5 KB
257ms
254ms
Script
application/javascript
13.32.121.29
Amazon.com
General
Full URL
https://assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/1837-34eb9da4.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.29 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-29.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
bec81b1853053f69bee514673d3d2b3ea729f4e8bb9d93e513e1173d6862b227

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
br
etag
W/"eea88d4e899bce6a692990c299ba631c"
age
358170
via
1.1 24ba6ae31527 (Varnish/7.5), 1.1 06a27d66e25d02ebcfb014b9d194016a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
x-amz-cf-id
fUp1tzNqU7-SlkiKFnkxcon0m6MmTVkrPFlCNQRODFXYWPrpSQiRcQ==
date
Wed, 02 Sep 2026 15:45:57 GMT
content-type
application/javascript
last-modified
Wed, 02 Sep 2026 01:36:34 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
vary
Accept-Encoding
GET
H2
200
3167-bd316714.js Show response
assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/
15 KB
6 KB
258ms
255ms
Script
application/javascript
13.32.121.29
Amazon.com
General
Full URL
https://assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/3167-bd316714.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.29 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-29.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
d2b1eb923ddade858143ec7f05947e89df039412693f6cefdad9c9a99ef74aa1

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
gzip
etag
W/"db3fbf6baf32b57087bcaf6f3029458f"
age
358974
via
1.1 c2856877bfae (Varnish/7.5), 1.1 06a27d66e25d02ebcfb014b9d194016a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
x-amz-cf-id
tCN_Yju75NpXTKxxB0Rnhv3rw8ubAqVJMpJ2yYiy40xjj9Y4Zpv8oA==
date
Wed, 02 Sep 2026 15:32:33 GMT
content-type
application/javascript
last-modified
Wed, 02 Sep 2026 01:36:34 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
vary
Accept-Encoding
GET
H2
200
8031-08bd7769.js Show response
assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/
8 KB
4 KB
259ms
256ms
Script
application/javascript
13.32.121.29
Amazon.com
General
Full URL
https://assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/8031-08bd7769.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.29 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-29.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
8b8550da8c13f3ab27157162f266369dedfaa3d31d50f7778a45495aba498dc2

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
br
etag
W/"1a2bdce334f2ccff57723463959f88e5"
age
358170
via
1.1 56e755a34cf9 (Varnish/7.5), 1.1 06a27d66e25d02ebcfb014b9d194016a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
x-amz-cf-id
3xDIv5P6eZz5fvcFHy8y4ekYsoDjQDKkKvO1A5oLIxjadH39p77NqA==
date
Wed, 02 Sep 2026 15:45:57 GMT
content-type
application/javascript
last-modified
Wed, 02 Sep 2026 01:36:34 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
vary
Accept-Encoding
GET
H2
200
8561-c3f98ed0.js Show response
assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/
9 KB
4 KB
264ms
261ms
Script
application/javascript
13.32.121.29
Amazon.com
General
Full URL
https://assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/8561-c3f98ed0.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.29 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-29.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
5a7d837d413eb7f87f71b2a66b8fe002bfb1899cad0c7724aed741d6069f0f97

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
br
etag
W/"bbe2000da825e148b86fc0d6900563ed"
age
358170
via
1.1 c2856877bfae (Varnish/7.5), 1.1 06a27d66e25d02ebcfb014b9d194016a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
x-amz-cf-id
OF2q6PJOHdRwfB7aYjk1EaX_p2i5PClpWmNXsneBvEy_ePdoT0jP2A==
date
Wed, 02 Sep 2026 15:45:57 GMT
content-type
application/javascript
last-modified
Wed, 02 Sep 2026 01:36:34 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
vary
Accept-Encoding
GET
H2
200
9524-eae2a04d.js Show response
assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/
45 KB
16 KB
259ms
256ms
Script
application/javascript
13.32.121.29
Amazon.com
General
Full URL
https://assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/9524-eae2a04d.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.29 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-29.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
dd192634cf2dd3338b73f1dea1ea131be3f22950d4dc2fea3942a853119ad0cc

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
gzip
etag
W/"329998e67b51cdd8049bc090be5306c7"
age
358974
via
1.1 24ba6ae31527 (Varnish/7.5), 1.1 06a27d66e25d02ebcfb014b9d194016a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
x-amz-cf-id
5-nX9UQeGsmnD65_XHAFrUJxDhWIT3aR4taYgfxon_3hksczNQg0RQ==
date
Wed, 02 Sep 2026 15:32:33 GMT
content-type
application/javascript
last-modified
Wed, 02 Sep 2026 01:36:34 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
vary
Accept-Encoding
GET
H2
200
fea4ac1291b1ab4b9e08331b030dbfca29ba761aae7f184704ffd867755688c0 Show response
scripts.webcontentassessor.com/scripts/
442 KB
122 KB
372ms
121ms
Script
application/javascript
54.192.35.118
Amazon.com
General
Full URL
https://scripts.webcontentassessor.com/scripts/fea4ac1291b1ab4b9e08331b030dbfca29ba761aae7f184704ffd867755688c0
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
54.192.35.118 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-54-192-35-118.fra56.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
d3e6fb798eb26cfb25d6100f39c0afd1310e4cfc6f7cde2215fca2748e5dafb4

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding, Origin
cache-control
max-age=3600,stale-if-error=86400,stale-while-revalidate=3600
content-encoding
gzip
x-amz-version-id
O2QofnqW1Pes9eqlt6uv0p4UZkDgKrvd
etag
W/"0d488024976fb76cfc8227641c238252"
age
1323
via
1.1 64fd5940fcefaae3736fad55ef5d289c.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
DM1zhncamS8WzCiCXwWHrbEQFub7BcnWva1fW6BNSSXw0uTLpQDBXQ==
date
Sun, 06 Sep 2026 18:53:24 GMT
content-type
application/javascript
last-modified
Sun, 06 Sep 2026 18:49:18 GMT
server
AmazonS3
x-amz-cf-pop
FRA56-P15
x-amz-server-side-encryption
AES256
GET

kabc-lg.svg
cdn.abcotvs.net/abcotv/assets/news/global/images/feature-header/
0
0


GET

kabc-sm.svg
cdn.abcotvs.net/abcotv/assets/news/global/images/feature-header/
0
0


GET

origin-kabc.png
cdn.abcotvs.net/abcotv/static/common/origins/
0
0


GET

19779720_090226-kabc-ontario-quake-tn.jpg
cdn.abcotvs.com/dip/images/
0
0


GET

2437274_092017-kabc-vod-quake-kits-vid.jpg
cdn.abcotvs.com/dip/images/
0
0


GET

19797681_090526-kabc-seal-beach-flooding-tn-img.jpg
cdn.abcotvs.com/dip/images/
0
0


GET

19799003_090626-kabc-ap-hurricanes.jpg
cdn.abcotvs.com/dip/images/
0
0


GET

19798536_090626-kabc-am-forecast-2-vid.jpg
cdn.abcotvs.com/dip/images/
0
0


GET

19798677_090626-kabc-5am-compton-earthquake-vid.jpg
cdn.abcotvs.com/dip/images/
0
0


GET

19799062_090526-kabc-8am-in-n-out-hero-vid.jpg
cdn.abcotvs.com/dip/images/
0
0


GET
H2
200
KABC_white.svg
assets-cdn.abcotvs.net/static/images/
2 KB
1 KB
258ms
255ms
Image
image/svg+xml
13.32.121.29
Amazon.com
General
Full URL
https://assets-cdn.abcotvs.net/static/images/KABC_white.svg
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.29 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-29.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
b77d6b68c1b0ce1abc47e070c9508ae458c2893a7a5cef58b7811158e25a6006

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
gzip
etag
W/"ccef5582d069a4af03f74712dbf07504"
age
12030355
via
1.1 56e755a34cf9 (Varnish/7.5), 1.1 06a27d66e25d02ebcfb014b9d194016a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
content-length
1014
x-amz-cf-id
ZG9xFo14los0Q9ZEtAKgwPBXdhQx0zNA7ReE3blJafIN1rp642M5-A==
date
Mon, 20 Apr 2026 13:29:32 GMT
content-type
image/svg+xml
last-modified
Mon, 13 Apr 2026 18:41:27 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
GET
H2
200
ios-white.svg
assets-cdn.abcotvs.net/static/images/devices/
10 KB
4 KB
275ms
273ms
Image
image/svg+xml
13.32.121.29
Amazon.com
General
Full URL
https://assets-cdn.abcotvs.net/static/images/devices/ios-white.svg
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.29 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-29.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
056de2f81ff61b778a0c192dbb098f9b0416e7e8f79b119e43d11248155e597f

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
gzip
etag
W/"0f3514a45d51f95167e5fe8b6a03bb60"
age
31279315
via
1.1 a3f84515b991 (Varnish/7.5), 1.1 06a27d66e25d02ebcfb014b9d194016a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
content-length
4053
x-amz-cf-id
LCMlgi7FzAcNd3HbrNvPqOfoAZxf3X7k7Lj7atw2NRgQcDJnvGLW0w==
date
Tue, 09 Sep 2025 18:33:32 GMT
content-type
image/svg+xml
last-modified
Thu, 04 Sep 2025 17:48:39 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
GET
H2
200
android-white.svg
assets-cdn.abcotvs.net/static/images/devices/
9 KB
10 KB
275ms
272ms
Image
image/svg+xml
13.32.121.29
Amazon.com
General
Full URL
https://assets-cdn.abcotvs.net/static/images/devices/android-white.svg
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.29 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-29.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
caaee3f7e731b7c3421b9501c6e9a886474954666fe9fb9a840523ebdd286186

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
W/"2dbfd5005b784c0679995578e0d2c355"
age
27139927
via
1.1 a3f84515b991 (Varnish/7.5), 1.1 06a27d66e25d02ebcfb014b9d194016a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
x-amz-cf-id
cJYxw3ZplYVVkcIMtmiebgu806LaX1o3oZ8RiIyHEeItaIX0P-Iu1g==
date
Mon, 27 Oct 2025 16:23:20 GMT
content-type
image/svg+xml
last-modified
Tue, 23 Sep 2025 21:55:53 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
vary
Accept-Encoding
GET
H2
200
_manifest.js Show response
assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/
10 KB
3 KB
275ms
273ms
Script
application/javascript
13.32.121.29
Amazon.com
General
Full URL
https://assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/_manifest.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.29 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-29.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
3c55f5a995896a2ba16808a9890e0b04a771c987359e55d878f940fd9d693a85

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
gzip
etag
W/"8349712d4e5e1dd87f74095ba6a19b55"
age
358973
via
1.1 56e755a34cf9 (Varnish/7.5), 1.1 06a27d66e25d02ebcfb014b9d194016a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
x-amz-cf-id
n241WAlUYmk2F4ThbluMv8r1T-XD1bE4m_p4gUdC8vAi00AwTU-Ibg==
date
Wed, 02 Sep 2026 15:32:34 GMT
content-type
application/javascript
last-modified
Wed, 02 Sep 2026 01:36:34 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
vary
Accept-Encoding
GET
H2
200
abcotv-1e22f9f4.js Show response
assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/
118 KB
41 KB
276ms
274ms
Script
application/javascript
13.32.121.29
Amazon.com
General
Full URL
https://assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/abcotv-1e22f9f4.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.29 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-29.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
a7a3d642f149d035b670cbe3a00dab0f83da7e9409862fc2da0cd5491bc20a48

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
gzip
etag
W/"26861b590405b8aca7cad6f74f8f3c88"
age
358974
via
1.1 24ba6ae31527 (Varnish/7.5), 1.1 06a27d66e25d02ebcfb014b9d194016a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
x-amz-cf-id
3wscnFpDGGEJiScz1RIC0lgX2-zZbdzd5036ruShnqzMqD9WgYxreg==
date
Wed, 02 Sep 2026 15:32:33 GMT
content-type
application/javascript
last-modified
Wed, 02 Sep 2026 01:36:34 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
vary
Accept-Encoding
GET
H2
200
prism-story-92391b39.js Show response
assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/
7 KB
4 KB
305ms
303ms
Script
application/javascript
13.32.121.29
Amazon.com
General
Full URL
https://assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/prism-story-92391b39.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.29 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-29.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
551fce1fd09bf3f992dbaf74428d7eb099f5a6dd30b063c12552b4f6adffd8dd

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
gzip
etag
W/"f6cef755df7b7264ba4cd6b9ba806a21"
age
358973
via
1.1 24ba6ae31527 (Varnish/7.5), 1.1 06a27d66e25d02ebcfb014b9d194016a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
x-amz-cf-id
96d29uwrO600FcBd_rJcV43elyYyNq5xTJIto7Dl1BNYcbymNZPLxw==
date
Wed, 02 Sep 2026 15:32:34 GMT
content-type
application/javascript
last-modified
Wed, 02 Sep 2026 01:36:35 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
vary
Accept-Encoding
GET
H2
200
otSDKStub.js Show response
cdn.cookielaw.org/consent/43227b6e-5025-42f8-baba-0fb73a46716b/
32 KB
11 KB
378ms
138ms
Script
application/javascript
104.18.87.42
Cloudflare
General
Full URL
https://cdn.cookielaw.org/consent/43227b6e-5025-42f8-baba-0fb73a46716b/otSDKStub.js
Requested by
Host: dcf.espn.com
URL: https://dcf.espn.com/TWDC-DTCI/prod/Bootstrap.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.18.87.42 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
b7dcd9bca642d42b30026dad18f424da41b1afdcc5510bc05795588c880209b8
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-md5
Xszxph0nGrNXQIwSCbLDfw==
access-control-expose-headers
x-ms-request-id,Server,x-ms-version,Content-Type,Content-Encoding,Cache-Control,ETag,Last-Modified,Content-MD5,x-ms-lease-status,x-ms-blob-type,Content-Length,Date,Transfer-Encoding, X-OneTrust-IsBot
content-encoding
gzip
cf-cache-status
HIT
etag
0x8DE1C92BE102DDD
age
57309
x-ms-lease-status
unlocked
x-content-type-options
nosniff
x-ms-version
2009-09-19
expires
Mon, 07 Sep 2026 19:15:27 GMT
date
Sun, 06 Sep 2026 19:15:27 GMT
content-type
application/javascript
last-modified
Wed, 05 Nov 2025 17:42:51 GMT
vary
accept-encoding
strict-transport-security
max-age=31536000; includeSubDomains; preload
x-onetrust-isbot
false
cache-control
public, max-age=86400
cross-origin-resource-policy
cross-origin, cross-origin
x-ms-request-id
a81e8640-301e-0040-6c25-d6ba64000000
cf-ray
a36fcd6f9dccd390-FRA
accept-ranges
bytes
access-control-allow-origin
*
x-ms-blob-type
BlockBlob
server
cloudflare
GET

otCCPAiab.js
cdn.espn.com/onetrust/
0
0


GET
H2
200
_manifest.js
assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/
0
0
258ms
258ms
Other
application/javascript
13.32.121.29
Amazon.com
General
Full URL
https://assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/_manifest.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.29 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-29.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
3c55f5a995896a2ba16808a9890e0b04a771c987359e55d878f940fd9d693a85

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
Sec-Purpose
prefetch
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
gzip
etag
W/"8349712d4e5e1dd87f74095ba6a19b55"
age
358973
via
1.1 56e755a34cf9 (Varnish/7.5), 1.1 06a27d66e25d02ebcfb014b9d194016a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
x-amz-cf-id
n241WAlUYmk2F4ThbluMv8r1T-XD1bE4m_p4gUdC8vAi00AwTU-Ibg==
date
Wed, 02 Sep 2026 15:32:34 GMT
content-type
application/javascript
last-modified
Wed, 02 Sep 2026 01:36:34 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
vary
Accept-Encoding
GET
H2
200
abcotv-1e22f9f4.js
assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/
0
0
255ms
255ms
Other
application/javascript
13.32.121.29
Amazon.com
General
Full URL
https://assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/abcotv-1e22f9f4.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.29 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-29.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
a7a3d642f149d035b670cbe3a00dab0f83da7e9409862fc2da0cd5491bc20a48

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
Sec-Purpose
prefetch
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
gzip
etag
W/"26861b590405b8aca7cad6f74f8f3c88"
age
358974
via
1.1 24ba6ae31527 (Varnish/7.5), 1.1 06a27d66e25d02ebcfb014b9d194016a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
x-amz-cf-id
3wscnFpDGGEJiScz1RIC0lgX2-zZbdzd5036ruShnqzMqD9WgYxreg==
date
Wed, 02 Sep 2026 15:32:33 GMT
content-type
application/javascript
last-modified
Wed, 02 Sep 2026 01:36:34 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
vary
Accept-Encoding
GET
H2
200
prism-story-92391b39.js
assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/
0
0
284ms
284ms
Other
application/javascript
13.32.121.29
Amazon.com
General
Full URL
https://assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/prism-story-92391b39.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.29 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-29.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
551fce1fd09bf3f992dbaf74428d7eb099f5a6dd30b063c12552b4f6adffd8dd

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
Sec-Purpose
prefetch
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
gzip
etag
W/"f6cef755df7b7264ba4cd6b9ba806a21"
age
358973
via
1.1 24ba6ae31527 (Varnish/7.5), 1.1 06a27d66e25d02ebcfb014b9d194016a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
x-amz-cf-id
96d29uwrO600FcBd_rJcV43elyYyNq5xTJIto7Dl1BNYcbymNZPLxw==
date
Wed, 02 Sep 2026 15:32:34 GMT
content-type
application/javascript
last-modified
Wed, 02 Sep 2026 01:36:35 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
vary
Accept-Encoding
GET
H2
200
TiemposText-Bold.woff2
s.abcnews.com/assets/dtci/fonts/klim/tiempos/
49 KB
50 KB
116ms
116ms
Font
application/octet-stream
13.32.121.2
Amazon.com
General
Full URL
https://s.abcnews.com/assets/dtci/fonts/klim/tiempos/TiemposText-Bold.woff2
Requested by
Host: assets-cdn.abcotvs.net
URL: https://assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/css/fusion-75eda2ba.css
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.2 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-2.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
aeffec31a76a877868be2afe8133a28a33954cccbac047671f75f7fd97c9112b

Request headers

Origin
https://abc7.com
sec-ch-ua-platform
"Linux"
Referer
https://assets-cdn.abcotvs.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
3000
x-amz-version-id
null
etag
"cae7c9da8746820f89c5919e8652632f"
age
173
access-control-allow-methods
GET
x-amz-meta-user-agent-id
abcnewssite@s-0da66bcd175040bb8
x-cache
Hit from cloudfront
x-amz-cf-id
cFYVm8F7KPRZji05vm65JawoMAcHoW30t5vkgGZ--J-dxPALKxc6-A==
date
Sun, 06 Sep 2026 19:15:27 GMT
content-type
application/octet-stream
last-modified
Fri, 11 Oct 2019 19:30:42 GMT
x-amz-meta-user-agent
AWSTransfer
vary
Origin,Access-Control-Request-Headers,Access-Control-Request-Method,Accept-Encoding
via
1.1 5fa65194b963365c20fbd28444032cfc.cloudfront.net (CloudFront)
accept-ranges
bytes
access-control-allow-origin
*
content-length
50490
x-amz-cf-pop
FRA60-P1
server
AmazonS3
GET
H2
200
geo Show response
pinpoint.espn.com/
520 B
637 B
625ms
203ms
XHR
application/json
100.60.116.23
Amazon.com
General
Full URL
https://pinpoint.espn.com/geo
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
100.60.116.23 Ashburn, United States, ASN14618 (AMAZON-AES - Amazon.com, Inc., US),
Reverse DNS
ec2-100-60-116-23.compute-1.amazonaws.com
Software
/
Resource Hash
d8e4261cad25114e7cbb2c772087e22dfd8d01279759fdbb3e87a20585fd464b

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
Accept
application/json, text/plain, */*
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

access-control-allow-origin
https://abc7.com
content-length
520
date
Sun, 06 Sep 2026 19:15:28 GMT
content-type
application/json
vary
origin
GET

-1.jsonp
prod.gatekeeper.us-abc.symphony.edgedatg.go.com/vp2/ws/utils/2021/geo/video/geolocation/201/001/gt/
0
0


GET
H2
200
abc_news Show response
pcs.bamgrid.com/v1/
813 B
1 KB
374ms
125ms
Fetch
application/json
13.226.244.19
Amazon.com
General
Full URL
https://pcs.bamgrid.com/v1/abc_news?namespaces=web&brand=google&platform=chrome
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.226.244.19 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-226-244-19.fra56.r.cloudfront.net
Software
/
Resource Hash
f1fd63ed4b43993109dfeba36e0e24b615dde97525c2cbd968c21f5fbc418def

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
600
x-request-id
2a07524828a6b5db021d3ded4e53af1e
access-control-expose-headers
x-request-id, x-bamtech-region, date
age
158589
access-control-allow-methods
GET, POST, PUT, PATCH, DELETE, OPTIONS
x-bypass-cache
false
x-cache
Hit from cloudfront
x-amz-cf-id
lIvbgOtLYsYiULknpN1CQlNpfyn3Z7iD9Cb4FcPAZzQn1ri2r1ds8w==
date
Fri, 04 Sep 2026 23:12:18 GMT
content-type
application/json
vary
origin
cache-control
s-maxage=31536000
access-control-allow-credentials
true
x-bamtech-region
eu-central-1
via
1.1 ede4657ca75ee1968129a6a3c26144b0.cloudfront.net (CloudFront)
access-control-allow-origin
https://abc7.com
content-length
813
x-amz-cf-pop
FRA56-P14
GET

-1.jsonp
prod.gatekeeper.us-abc.symphony.edgedatg.go.com/vp2/ws/utils/2021/geo/video/geolocation/201/001/gt/
0
0


GET
H2
200
43227b6e-5025-42f8-baba-0fb73a46716b.json Show response
cdn.cookielaw.org/consent/43227b6e-5025-42f8-baba-0fb73a46716b/
5 KB
2 KB
371ms
134ms
XHR
application/json
104.18.87.42
Cloudflare
General
Full URL
https://cdn.cookielaw.org/consent/43227b6e-5025-42f8-baba-0fb73a46716b/43227b6e-5025-42f8-baba-0fb73a46716b.json
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.18.87.42 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
e1b1f83a6e6f144fad9e0cdf4af3a0236239b45e9dfba2d192b638f1313ef573
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-md5
ohzm0ebF9Jzq13hvJlgxcQ==
access-control-expose-headers
x-ms-request-id,Server,x-ms-version,Content-Type,Content-Encoding,Cache-Control,ETag,Last-Modified,Content-MD5,x-ms-lease-status,x-ms-blob-type,Content-Length,Date,Transfer-Encoding, X-OneTrust-IsBot
content-encoding
gzip
cf-cache-status
HIT
etag
0x8DE1C92BCEA83B1
age
40519
x-ms-lease-status
unlocked
x-content-type-options
nosniff
x-ms-version
2009-09-19
expires
Mon, 07 Sep 2026 19:15:28 GMT
date
Sun, 06 Sep 2026 19:15:28 GMT
content-type
application/json
last-modified
Wed, 05 Nov 2025 17:42:49 GMT
vary
accept-encoding
strict-transport-security
max-age=31536000; includeSubDomains; preload
x-onetrust-isbot
true
cache-control
public, max-age=86400
cross-origin-resource-policy
cross-origin, cross-origin
x-ms-request-id
46747020-201e-001b-475b-e1bd18000000
cf-ray
a36fcd745e04d2c3-FRA
accept-ranges
bytes
access-control-allow-origin
*
x-ms-blob-type
BlockBlob
server
cloudflare
GET
H2
200
nr-spa-1216.min.js Show response
js-agent.newrelic.com/
49 KB
17 KB
364ms
118ms
Script
application/javascript
162.247.243.39
Fastly
General
Full URL
https://js-agent.newrelic.com/nr-spa-1216.min.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
162.247.243.39 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
/
Resource Hash
545156adeae44dadc82b98d504f805ebe77fb79c928ef34eed1057bb9d4cb8fe
Security Headers
Name Value
Strict-Transport-Security max-age=300

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=300
cache-control
public, max-age=31536000, stale-while-revalidate=86400, stale-if-error=86400
content-encoding
br
etag
"63e2df852d15ab21d7ff8fc4363222e8"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
x-cache
HIT
content-length
17587
date
Sun, 06 Sep 2026 19:15:28 GMT
last-modified
Wed, 18 Oct 2023 21:31:16 GMT
content-type
application/javascript
x-served-by
cache-par-lfpb1150051-PAR
x-cache-hits
26615
vary
Accept-Encoding
GET
H2
200
/ Show response
zn5hsliyrlhlj7ndr-abcotv.siteintercept.qualtrics.com/WRSiteInterceptEngine/
10 KB
5 KB
415ms
137ms
Script
application/javascript
104.17.208.240
Cloudflare
General
Full URL
https://zn5hsliyrlhlj7ndr-abcotv.siteintercept.qualtrics.com/WRSiteInterceptEngine/?Q_ZID=ZN_5hSLIyrLhlJ7ndr&Q_LOC=https%3A%2F%2Fabc7.com%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F&t=1788722127748
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.17.208.240 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
5476b2508c09ec909c979c8e197c0eec5717e7647e506fde98c48839c823f92a
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
cf-cache-status
HIT
etag
W/"29c5-PHjKAzgUfX1P8aKT8eogmDKFaQg"
age
43258
x-content-type-options
nosniff
date
Sun, 06 Sep 2026 19:15:28 GMT
edge-control
max-age=604800
content-type
application/javascript; charset=utf-8
vary
Accept-Encoding
access-control-allow-headers
Origin, X-Requested-With, Content-Type, Accept
strict-transport-security
max-age=31536000; includeSubDomains; preload
cache-control
public, max-age=3600, s-maxage=604800
timing-allow-origin
*
referrer-policy
strict-origin-when-cross-origin
content-security-policy-report-only
frame-ancestors 'self' *.qualtrics.com *.my.salesforce.com *.visualforce.com *.visual.force.com *.lightning.force.com; report-uri https://sjc1.qualtrics.com/csp-report
cf-ray
a36fcd748ad4353c-FRA
permissions-policy
camera=(), geolocation=(), microphone=()
access-control-allow-origin
*
server
cloudflare
GET

favicon.ico
cdn.abcotvs.net/abcotv/assets/news/kabc/images/logos/
0
0


GET
H2
200
abc_news Show response
pcs.bamgrid.com/v1/
317 B
850 B
123ms
123ms
XHR
application/json
13.226.244.19
Amazon.com
General
Full URL
https://pcs.bamgrid.com/v1/abc_news?namespaces=hive-dmp
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.226.244.19 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-226-244-19.fra56.r.cloudfront.net
Software
/
Resource Hash
5ba40c778ca2637c7c6e8c2749c330a77f64a2f5bddce2847494799c7556fcb2

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
600
x-request-id
c2319daac12957ec1b452d95e4ffcb14
access-control-expose-headers
x-request-id, x-bamtech-region, date
age
158490
access-control-allow-methods
GET, POST, PUT, PATCH, DELETE, OPTIONS
x-bypass-cache
false
x-cache
Hit from cloudfront
x-amz-cf-id
rcf7DfrT28Bk7dCOrzGH7FtIpNBFzY5fCV004M2eeHntn3L78Fvb8Q==
date
Fri, 04 Sep 2026 23:13:58 GMT
content-type
application/json
vary
origin
cache-control
s-maxage=31536000
access-control-allow-credentials
true
x-bamtech-region
eu-central-1
via
1.1 ede4657ca75ee1968129a6a3c26144b0.cloudfront.net (CloudFront)
access-control-allow-origin
https://abc7.com
content-length
317
x-amz-cf-pop
FRA56-P14
GET
H2
200
playback-service.js Show response
hiveplayer-static.bamgrid.com/artifacts/hive/playback-service/26.9.0-iridessa/all_browser_es5/
679 KB
116 KB
399ms
144ms
Script
application/javascript
99.84.152.107
Amazon.com
General
Full URL
https://hiveplayer-static.bamgrid.com/artifacts/hive/playback-service/26.9.0-iridessa/all_browser_es5/playback-service.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
99.84.152.107 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-99-84-152-107.fra56.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
39a603a6d8b689bca8c69c62c332f26d60f5682c959b5e6643e3655daafb54b6

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-encoding
gzip
etag
W/"701aa6318d44db2dc036a8a5f3b83429"
x-amz-version-id
9amJkpwXe0Fe5WoDuyqG.SfeZkOAdCPp
age
28
via
1.1 2694fffaa67bb0ec65670b8dce8dcd24.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
nsiKeYRg-gjix8A-kfRwAf8DUU3Zf4FTMeJuOrGYizf8diMBcLj8KQ==
date
Sun, 06 Sep 2026 19:15:01 GMT
content-type
application/javascript
last-modified
Mon, 10 Aug 2026 17:43:29 GMT
server
AmazonS3
x-amz-cf-pop
FRA56-P13
x-amz-server-side-encryption
AES256
GET
H2
200
otBannerSdk.js Show response
cdn.cookielaw.org/scripttemplates/202509.1.0/
503 KB
122 KB
131ms
131ms
Script
application/javascript
104.18.87.42
Cloudflare
General
Full URL
https://cdn.cookielaw.org/scripttemplates/202509.1.0/otBannerSdk.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.18.87.42 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
e4a4e646988da9ff17c1390f40929de6dbad336b137a818a80163075807184af
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-md5
hR2rJrfQlXodAcvjDvQHJQ==
access-control-expose-headers
x-ms-request-id,Server,x-ms-version,Content-Type,Content-Encoding,ETag,Last-Modified,Content-MD5,x-ms-lease-status,x-ms-blob-type,Content-Length,Date,Transfer-Encoding
content-encoding
gzip
x-ms-version
2009-09-19
etag
0x8DDFFC67CB575C5
x-ms-lease-status
unlocked
age
1520
cf-cache-status
HIT
x-content-type-options
nosniff
date
Sun, 06 Sep 2026 19:15:28 GMT
content-type
application/javascript
last-modified
Tue, 30 Sep 2025 02:10:11 GMT
vary
accept-encoding
strict-transport-security
max-age=31536000; includeSubDomains; preload
cache-control
max-age=86400
cross-origin-resource-policy
cross-origin
x-ms-request-id
f8bad80d-401e-0029-4235-dee5c8000000
cf-ray
a36fcd752887d390-FRA
accept-ranges
bytes
access-control-allow-origin
*
content-length
124198
x-ms-blob-type
BlockBlob
server
cloudflare
GET
H2
200
881.73d90aac6e002319d3e8.chunk.js Show response
siteintercept.qualtrics.com/dxjsmodule/
52 KB
18 KB
221ms
215ms
Script
application/javascript
104.17.208.240
Cloudflare
General
Full URL
https://siteintercept.qualtrics.com/dxjsmodule/881.73d90aac6e002319d3e8.chunk.js?Q_CLIENTVERSION=2.56.0&Q_CLIENTTYPE=web&Q_BRANDID=abc7.com
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.17.208.240 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
183bf373d62b948f0d10454ccf8cb95872706fa86a032d23927f3b716e0a5a70
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
cf-cache-status
HIT
etag
W/"cf3d-1a035708268"
age
445563
x-content-type-options
nosniff
date
Sun, 06 Sep 2026 19:15:28 GMT
edge-control
max-age=604800
content-type
application/javascript
last-modified
Mon, 24 Aug 2026 20:22:41 GMT
vary
Accept-Encoding
access-control-allow-headers
Origin, X-Requested-With, Content-Type, Accept
strict-transport-security
max-age=31536000; includeSubDomains; preload
cache-control
public, max-age=604800, s-maxage=604800
timing-allow-origin
*
referrer-policy
strict-origin-when-cross-origin
content-security-policy-report-only
frame-ancestors 'self' *.qualtrics.com *.my.salesforce.com *.visualforce.com *.visual.force.com *.lightning.force.com; report-uri https://sjc1.qualtrics.com/csp-report
cf-ray
a36fcd757e00353c-FRA
permissions-policy
camera=(), geolocation=(), microphone=()
access-control-allow-origin
*
server
cloudflare
GET
H2
200
626.ed883c3515d3b599438f.chunk.js Show response
siteintercept.qualtrics.com/dxjsmodule/
147 KB
39 KB
139ms
134ms
Script
application/javascript
104.17.208.240
Cloudflare
General
Full URL
https://siteintercept.qualtrics.com/dxjsmodule/626.ed883c3515d3b599438f.chunk.js?Q_CLIENTVERSION=2.56.0&Q_CLIENTTYPE=web&Q_BRANDID=abc7.com
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.17.208.240 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
be8732f78da30d4f74a7edeb7e45700f30676a461da4ded0aa6050d43f33fb20
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
cf-cache-status
HIT
etag
W/"24bb7-1a035708268"
age
323348
x-content-type-options
nosniff
date
Sun, 06 Sep 2026 19:15:28 GMT
edge-control
max-age=604800
content-type
application/javascript
last-modified
Mon, 24 Aug 2026 20:22:41 GMT
vary
Accept-Encoding
access-control-allow-headers
Origin, X-Requested-With, Content-Type, Accept
strict-transport-security
max-age=31536000; includeSubDomains; preload
cache-control
public, max-age=604800, s-maxage=604800
timing-allow-origin
*
referrer-policy
strict-origin-when-cross-origin
content-security-policy-report-only
frame-ancestors 'self' *.qualtrics.com *.my.salesforce.com *.visualforce.com *.visual.force.com *.lightning.force.com; report-uri https://sjc1.qualtrics.com/csp-report
cf-ray
a36fcd757e05353c-FRA
permissions-policy
camera=(), geolocation=(), microphone=()
access-control-allow-origin
*
server
cloudflare
GET
H/1.1
200
8d01ff17d1 Show response
bam.nr-data.net/1/
98 B
618 B
456ms
214ms
Script
text/javascript
162.247.243.29
Fastly
General
Full URL
https://bam.nr-data.net/1/8d01ff17d1?a=415461361&sa=1&v=1216.487a282&t=Unnamed%20Transaction&rst=2414&ck=1&ref=https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/&be=1235&fe=1990&dc=1984&af=err,xhr,stn,ins,spa&perf=%7B%22timing%22:%7B%22of%22:1788722125757,%22n%22:0,%22f%22:1,%22dn%22:1,%22dne%22:9,%22c%22:9,%22s%22:65,%22ce%22:259,%22rq%22:259,%22rp%22:592,%22rpe%22:690,%22dl%22:596,%22di%22:1273,%22ds%22:1985,%22de%22:1985,%22dc%22:1990,%22l%22:1990,%22le%22:1992%7D,%22navigation%22:%7B%7D%7D&fp=1308&fcp=1308&jsonp=NREUM.setToken
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_128_GCM
Server
162.247.243.29 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
/
Resource Hash
f6d26e5b4ad0544677b9d8b4ba4fd8894beed9bb6faf0e18be93ee8a38b19c73

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

access-control-expose-headers
Date
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
Connection
keep-alive
access-control-allow-methods
GET, POST, PUT, HEAD, OPTIONS
access-control-allow-credentials
true
access-control-allow-origin
*
Content-Length
98
date
Sun, 06 Sep 2026 19:15:28 GMT
content-type
text/javascript
x-served-by
cache-lon420110-LON
nr-rate-limited
allowed
GET
H2
200
en.json Show response
cdn.cookielaw.org/consent/43227b6e-5025-42f8-baba-0fb73a46716b/01991628-d4e6-79f1-82d7-9c523fc1c47f/
304 KB
48 KB
152ms
152ms
Fetch
application/json
104.18.87.42
Cloudflare
General
Full URL
https://cdn.cookielaw.org/consent/43227b6e-5025-42f8-baba-0fb73a46716b/01991628-d4e6-79f1-82d7-9c523fc1c47f/en.json
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.18.87.42 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
297fe25af91ac264d11a4d8a15ce3e46c4a06b5bc25469714ef48725b577e9eb
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-md5
iqOZYdteoJcIyPj7XqXP3w==
access-control-expose-headers
x-ms-request-id,Server,x-ms-version,Content-Type,Content-Encoding,Cache-Control,ETag,Last-Modified,Content-MD5,x-ms-lease-status,x-ms-blob-type,Content-Length,Date,Transfer-Encoding, X-OneTrust-IsBot
content-encoding
gzip
cf-cache-status
HIT
etag
0x8DE1C92BF2DCAC3
age
51137
x-ms-lease-status
unlocked
x-content-type-options
nosniff
x-ms-version
2009-09-19
expires
Mon, 07 Sep 2026 19:15:28 GMT
date
Sun, 06 Sep 2026 19:15:28 GMT
content-type
application/json
last-modified
Wed, 05 Nov 2025 17:42:53 GMT
vary
accept-encoding
strict-transport-security
max-age=31536000; includeSubDomains; preload
x-onetrust-isbot
true
cache-control
public, max-age=86400
cross-origin-resource-policy
cross-origin, cross-origin
x-ms-request-id
4367e047-801e-00f8-5295-b25897000000
cf-ray
a36fcd77088fd2c3-FRA
accept-ranges
bytes
access-control-allow-origin
*
x-ms-blob-type
BlockBlob
server
cloudflare
POST
H2
200
Targeting.php Show response
siteintercept.qualtrics.com/WRSiteInterceptEngine/
57 B
227 B
227ms
226ms
XHR
text/plain
104.17.208.240
Cloudflare
General
Full URL
https://siteintercept.qualtrics.com/WRSiteInterceptEngine/Targeting.php?Q_ZoneID=ZN_5hSLIyrLhlJ7ndr&Q_CLIENTVERSION=2.56.0&Q_CLIENTTYPE=web
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.17.208.240 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
191c90e801eda262d5d782185a06b18569d22fa74974b8e907900f3a32543ff9
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
Content-type
application/x-www-form-urlencoded
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains; preload
cache-control
must-revalidate, max-age=300
timing-allow-origin
*
content-encoding
br
cf-cache-status
DYNAMIC
trace-id
26020e96b1c3e91d
access-control-allow-credentials
true
referrer-policy
strict-origin-when-cross-origin
x-content-type-options
nosniff
cf-ray
a36fcd770b70353c-FRA
permissions-policy
camera=(), geolocation=(), microphone=()
access-control-allow-origin
https://abc7.com
date
Sun, 06 Sep 2026 19:15:28 GMT
content-type
text/plain; charset=UTF-8
server
cloudflare
GET
H2
200
abc_news Show response
pcs.bamgrid.com/v1/
1 KB
1 KB
125ms
124ms
XHR
application/json
13.226.244.19
Amazon.com
General
Full URL
https://pcs.bamgrid.com/v1/abc_news?brand=google&platform=chrome&os=linux&namespaces=hive-dmp,ads,pqm
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.226.244.19 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-226-244-19.fra56.r.cloudfront.net
Software
/
Resource Hash
3005cd8a92a5c20d9a596716643de6e8f91d9b5360bf2964ffaa13b5bdf6607c

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
600
x-request-id
212047624040d6a514108a748cb31519
access-control-expose-headers
x-request-id, x-bamtech-region, date
content-encoding
gzip
age
104938
access-control-allow-methods
GET, POST, PUT, PATCH, DELETE, OPTIONS
x-bypass-cache
false
x-cache
Hit from cloudfront
x-amz-cf-id
_A7Xygn9YOxS2Xn73edlgU1TRlH3eQDa2WgHSVUMGAXyYZiM1wDo6g==
date
Sat, 05 Sep 2026 14:06:30 GMT
content-type
application/json
vary
origin
cache-control
s-maxage=31536000
access-control-allow-credentials
true
x-bamtech-region
eu-central-1
via
1.1 ede4657ca75ee1968129a6a3c26144b0.cloudfront.net (CloudFront)
access-control-allow-origin
https://abc7.com
x-amz-cf-pop
FRA56-P14
POST
H/1.1
200
8d01ff17d1 Show response
bam.nr-data.net/events/1/
24 B
355 B
208ms
207ms
XHR
image/gif
162.247.243.29
Fastly
General
Full URL
https://bam.nr-data.net/events/1/8d01ff17d1?a=415461361&sa=1&v=1216.487a282&t=Unnamed%20Transaction&rst=2880&ck=1&ref=https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_128_GCM
Server
162.247.243.29 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
/
Resource Hash
0c9cf152a0ad00d4f102c93c613c104914be5517ac8f8e0831727f8bfbe8b300

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
content-type
text/plain
sec-ch-ua-mobile
?0

Response headers

Connection
keep-alive
access-control-allow-credentials
true
access-control-allow-methods
GET, POST, PUT, HEAD, OPTIONS
access-control-allow-origin
https://abc7.com
Content-Length
24
date
Sun, 06 Sep 2026 19:15:28 GMT
content-type
image/gif
x-served-by
cache-lon420143-LON
nr-rate-limited
allowed
GET
H2
200
otGPP.js Show response
cdn.cookielaw.org/scripttemplates/202509.1.0/
151 KB
22 KB
132ms
131ms
Script
application/javascript
104.18.87.42
Cloudflare
General
Full URL
https://cdn.cookielaw.org/scripttemplates/202509.1.0/otGPP.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.18.87.42 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
fe740bc7fa6bb34ca8821e99e643ca68c05caee080c2b3f6b80706a6e567c407
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-md5
pwblQr7bhMnD4K+yMD1EHg==
access-control-expose-headers
x-ms-request-id,Server,x-ms-version,Content-Type,ETag,Last-Modified,Content-MD5,x-ms-lease-status,x-ms-blob-type,Content-Length,Date,Transfer-Encoding
x-ms-version
2009-09-19
x-ms-lease-status
unlocked
cf-cache-status
HIT
age
53683
content-encoding
gzip
x-content-type-options
nosniff
date
Sun, 06 Sep 2026 19:15:28 GMT
content-type
application/javascript
last-modified
Tue, 30 Sep 2025 02:10:15 GMT
strict-transport-security
max-age=31536000; includeSubDomains; preload
cache-control
max-age=86400
cross-origin-resource-policy
cross-origin
x-ms-request-id
d14e4fa6-401e-0083-0f1b-d13327000000
cf-ray
a36fcd788b8ed390-FRA
access-control-allow-origin
*
x-ms-blob-type
BlockBlob
server
cloudflare
GET
H2
200
weather Show response
api.abcotvs.com/v4/kabc/
629 B
923 B
447ms
153ms
XHR
application/json
3.173.161.33
Amazon.com
General
Full URL
https://api.abcotvs.com/v4/kabc/weather?key=otv.web.kabc.weather
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.173.161.33 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-173-161-33.ams56.r.cloudfront.net
Software
/
Resource Hash
caffb493a87dbf3234eb6d3c24706a4bf486da9239ba3f901fa18b2ce478f260

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=600, public, s-maxage=600
age
60
via
1.1 466c3546cf43688a93575672b4bae798.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
content-length
629
x-amz-cf-id
-O43rJwmZ8yKsrDXTl-YISWkE6ekwILD-W19B2nMIqRouyHQ4vSPyw==
date
Sun, 06 Sep 2026 19:14:29 GMT
content-type
application/json
x-amz-cf-pop
AMS56-P1
GET
H2
200
sdk.js Show response
cdn.disneyaccount.com/v5/
216 KB
54 KB
376ms
138ms
Script
text/javascript
3.173.161.103
Amazon.com
General
Full URL
https://cdn.disneyaccount.com/v5/sdk.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.173.161.103 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-173-161-103.ams56.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
7a04597d976ee1b2772dd733345c922bc6e113b2c2ce70ddbed53d5bcf07b611

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-encoding
gzip
etag
W/"626a14f7ab1bc670101b3c9ddf94f89a"
x-amz-version-id
null
age
65553
via
1.1 274ec33f25329170e853def437452832.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
BIi5BMTMf9b1BleplrLN5OItMcyhNUo2qBys-ulxjUTqDTJRqP5a4g==
date
Sun, 06 Sep 2026 01:02:57 GMT
content-type
text/javascript
last-modified
Wed, 12 Aug 2026 20:02:28 GMT
server
AmazonS3
x-amz-cf-pop
AMS56-P1
x-amz-server-side-encryption
AES256
GET
H2
200
serverComponent.php Show response
dcf.espn.com/TWDC-DTCI/prod/
812 B
693 B
691ms
156ms
Fetch
application/json
3.124.173.63
Amazon.com
General
Full URL
https://dcf.espn.com/TWDC-DTCI/prod/serverComponent.php?namespace=Bootstrapper&staticJsPath=/TWDC-DTCI/prod/code/&ClientID=2750&PageID=https%3A%2F%2Fabc7.com%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F%3Fcds%3Dn%26country%3Dbr%26region%3Dccpa%26gpc%3D0%26shouldFire%3Dy%26nAsyncNgeo%3Dn%26portal%3Dnews%26site%3Dkabc%26siteRegion%3D%26realHost%3Dabc7.com%26kpTlium%3Dn%26eventStep%3Dnon-ecom&custDomain=dcf.espn.com
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
3.124.173.63 Frankfurt am Main, Germany, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-3-124-173-63.eu-central-1.compute.amazonaws.com
Software
CloudFront /
Resource Hash
0ec8004a1424aa80258d4dc94ad06dbef5dbaaf491f3231e54e41e6a46d02ca1

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, no-store
content-encoding
gzip
via
1.1 85310f8b6878a9cfaa0218e021ae364e.cloudfront.net (CloudFront)
expires
Sun, 06 Sep 2026 19:15:28 GMT
alt-svc
h3=":443"; ma=86400
x-cache
Miss from cloudfront
x-amz-cf-id
V5SYB5mKxwp658sU9eXN3S0aOu9WLuO9DAWoWflHhuB7Q_yIC4CO-g==
date
Sun, 06 Sep 2026 19:15:29 GMT
content-type
application/json
vary
Accept-Encoding
server
CloudFront
x-amz-cf-pop
FRA56-P7
access-control-allow-origin
*
GET
H2
200
/
abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/kabc/
Redirect Chain
  • https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/kabc
  • https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/kabc/
6 KB
6 KB
263ms
263ms
Image
text/html
18.65.39.76
Amazon.com
General
Full URL
https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/kabc/
Protocol
H2
Server
18.65.39.76 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-18-65-39-76.ams1.r.cloudfront.net
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
Referer
https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/

Response headers

cache-control
max-age=0
content-encoding
gzip
via
1.1 045d55468661252b6be78e701e36b492.cloudfront.net (CloudFront)
expires
Sun, 06 Sep 2026 19:15:38 GMT
x-cache
Miss from cloudfront
x-amz-cf-id
W4unO5TPhhtjnK688Mkh7bAXM5a6Ed9AqrSWyMZNC3pHa9Pjsoixew==
date
Sun, 06 Sep 2026 19:15:29 GMT
content-type
text/html; charset=utf-8
last-modified
Sun, 06 Sep 2026 19:15:38 GMT
server
nginx
x-amz-cf-pop
AMS1-P1
vary
Accept-Encoding

Redirect headers

cache-control
max-age=3600
location
https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/kabc/
content-encoding
gzip
via
1.1 045d55468661252b6be78e701e36b492.cloudfront.net (CloudFront)
expires
Sun, 06 Sep 2026 20:15:28 GMT
x-cache
Miss from cloudfront
x-amz-cf-id
6bQD5OChR_5ncGeF8k3p-4aiCaErJ29OLGIL1DruMRTMxYvuJuoMjg==
date
Sun, 06 Sep 2026 19:15:28 GMT
content-type
text/html
vary
Accept-Encoding
server
nginx
x-amz-cf-pop
AMS1-P1
GET
H2
200
prod.json Show response
client-sdk-configs.bamgrid.com/bam-sdk/v7.0/disney-entertainment-a03f82b0/browser/v35.3/linux/chrome/
70 KB
7 KB
683ms
438ms
Fetch
application/json
18.238.243.39
Amazon.com
General
Full URL
https://client-sdk-configs.bamgrid.com/bam-sdk/v7.0/disney-entertainment-a03f82b0/browser/v35.3/linux/chrome/prod.json
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
18.238.243.39 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-18-238-243-39.ams58.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
44ee1fb49dfaca2456c9ca07d2f7afe06c24f2f91c725338bf096173c63cc22d

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
accept
application/json
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
3000
content-encoding
gzip
x-amz-version-id
2svHxxWQNdsA8h4BVNIG4WINZeVCjrbg
etag
W/"f65e06d1d0795b477b29210dd1af09a7"
access-control-allow-methods
GET, HEAD
x-cache
RefreshHit from cloudfront
x-amz-meta-x-dataset-version
7.0.75
date
Sun, 06 Sep 2026 19:15:30 GMT
content-type
application/json
vary
Origin,Access-Control-Request-Headers,Access-Control-Request-Method,Accept-Encoding
last-modified
Tue, 25 Aug 2026 17:48:06 GMT
x-amz-cf-id
NdZKwgU80yucH6uzwHyJ9vmvwICsPKeTjad921z-x5WodvBlpRvIlA==
cache-control
max-age=1800, no-transform, public
x-amz-meta-x-sha1
b09cb9fe76ef0b41bf4bfb7767a134bb40066848
via
1.1 0a4b38fa4b7e435c9572519905d42268.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-amz-cf-pop
AMS58-P1
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H2
200
chartbeat.js Show response
static.chartbeat.com/js/
41 KB
17 KB
369ms
137ms
Script
application/x-javascript
18.245.63.132
Amazon.com
General
Full URL
https://static.chartbeat.com/js/chartbeat.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
18.245.63.132 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-18-245-63-132.fra60.r.cloudfront.net
Software
openresty /
Resource Hash
a613444e09a3ec07bef1e16e21a31193a624c1b213e75e32767e303dd4cd7bb1

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=86400
content-encoding
gzip
etag
W/"6a62ac10-a310"
age
56898
cross-origin-resource-policy
cross-origin
via
1.1 2b92d172bc628dd9c34a8c262218ac02.cloudfront.net (CloudFront)
expires
Mon, 07 Sep 2026 03:27:11 GMT
x-cache
Hit from cloudfront
x-amz-cf-id
J7w8FZ4vB6DJLYDzAfqUjcvgy7nfQ7weVFFqzaA4TdC2dFiwmOPZ0A==
date
Sun, 06 Sep 2026 03:27:11 GMT
content-type
application/x-javascript
last-modified
Fri, 24 Jul 2026 00:04:32 GMT
server
openresty
x-amz-cf-pop
FRA60-P5
vary
Accept-Encoding
GET
H2
200
loader.js Show response
cdn.taboola.com/libtrc/abcotvweb-network/
1 MB
329 KB
358ms
119ms
Script
application/javascript
151.101.193.44
Fastly
General
Full URL
https://cdn.taboola.com/libtrc/abcotvweb-network/loader.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
AmazonS3 /
Resource Hash
fb8bf8224e7a648b98b506505a463318b0a02de560acd7f799ca0316cccd317e

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-fastly-object-storage
false
content-encoding
gzip
etag
"8b8786f3ac3d39b8e73a8efa9760caa8"
x-amz-version-id
_oUsfPo1oLiRW5nWVU9DNytyj4lMNBNy
age
84
x-cache
HIT
date
Sun, 06 Sep 2026 19:15:29 GMT
last-modified
Sun, 06 Sep 2026 09:25:03 GMT
x-served-by
cache-lon4258-LON
x-cache-hits
1
content-type
application/javascript; charset=utf-8
x-amz-id-2
s277a2oGBm6e5xi70I0Zwgsb2riEeeaBnUTPTZWWZtgBXB03fnV+LoaWonrc5rCyS71Aa2opoqZvevIVSY742v1iBdMrFUrE
x-amz-meta-x-tbl-source
kfc-purge-prod
vary
Accept-Encoding
x-amz-replication-status
FAILED
cache-control
private,max-age=14401
x-timer
S1788722129.137938,VS0,VE1
via
1.1 varnish
x-amz-request-id
MCVVFDYRQ862DTFC
accept-ranges
bytes
access-control-allow-origin
*
abp
88
content-length
336141
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H2
200
otFlat.json Show response
cdn.cookielaw.org/scripttemplates/202509.1.0/assets/
15 KB
3 KB
149ms
149ms
Fetch
application/json
104.18.87.42
Cloudflare
General
Full URL
https://cdn.cookielaw.org/scripttemplates/202509.1.0/assets/otFlat.json
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.18.87.42 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
1e05381160d3bc508aae36ca5a6f0ade2d359ebd1f3d2a051b7c6de6b151bba7
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-md5
38Jz5Uh6R2Fk5d9Ary2NyA==
access-control-expose-headers
x-ms-request-id,Server,x-ms-version,Content-Type,Content-Encoding,ETag,Last-Modified,Content-MD5,x-ms-lease-status,x-ms-blob-type,Content-Length,Date,Transfer-Encoding
content-encoding
gzip
x-ms-version
2009-09-19
etag
0x8DDFFC6794F1845
x-ms-lease-status
unlocked
age
71879
cf-cache-status
HIT
x-content-type-options
nosniff
date
Sun, 06 Sep 2026 19:15:28 GMT
content-type
application/json
last-modified
Tue, 30 Sep 2025 02:10:06 GMT
vary
accept-encoding
strict-transport-security
max-age=31536000; includeSubDomains; preload
cache-control
max-age=86400
cross-origin-resource-policy
cross-origin
x-ms-request-id
50ad2d74-801e-007b-7f1e-29f83a000000
cf-ray
a36fcd79b99ad2c3-FRA
accept-ranges
bytes
access-control-allow-origin
*
content-length
3145
x-ms-blob-type
BlockBlob
server
cloudflare
GET
H2
200
otPcCenter.json Show response
cdn.cookielaw.org/scripttemplates/202509.1.0/assets/v2/
66 KB
13 KB
137ms
137ms
Fetch
application/json
104.18.87.42
Cloudflare
General
Full URL
https://cdn.cookielaw.org/scripttemplates/202509.1.0/assets/v2/otPcCenter.json
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.18.87.42 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
c9ddcfec65756882dfadc85d82527e60c07ecf546434e16ce478659deb03754a
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-md5
fuuIXrDfP6VQtHh4AGyesg==
access-control-expose-headers
x-ms-request-id,Server,x-ms-version,Content-Type,Content-Encoding,ETag,Last-Modified,Content-MD5,x-ms-lease-status,x-ms-blob-type,Content-Length,Date,Transfer-Encoding
content-encoding
gzip
x-ms-version
2009-09-19
etag
0x8DDFFC67A88D0B5
x-ms-lease-status
unlocked
age
60716
cf-cache-status
HIT
x-content-type-options
nosniff
date
Sun, 06 Sep 2026 19:15:28 GMT
content-type
application/json
last-modified
Tue, 30 Sep 2025 02:10:08 GMT
vary
accept-encoding
strict-transport-security
max-age=31536000; includeSubDomains; preload
cache-control
max-age=86400
cross-origin-resource-policy
cross-origin
x-ms-request-id
593c63a2-a01e-0028-5768-dde435000000
cf-ray
a36fcd79b99fd2c3-FRA
accept-ranges
bytes
access-control-allow-origin
*
content-length
13402
x-ms-blob-type
BlockBlob
server
cloudflare
GET
H2
200
otCommonStyles.css Show response
cdn.cookielaw.org/scripttemplates/202509.1.0/assets/
26 KB
5 KB
147ms
147ms
Fetch
text/css
104.18.87.42
Cloudflare
General
Full URL
https://cdn.cookielaw.org/scripttemplates/202509.1.0/assets/otCommonStyles.css
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.18.87.42 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
2cc804e7b18cb3d2143d8a44db9d4467e349734d6a384bc089e4c31d3998959a
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-md5
eLyXdZf+bqdC5B3OZljzGQ==
access-control-expose-headers
x-ms-request-id,Server,x-ms-version,Content-Type,ETag,Last-Modified,Content-MD5,x-ms-lease-status,x-ms-blob-type,Content-Length,Date,Transfer-Encoding
x-ms-version
2009-09-19
x-ms-lease-status
unlocked
cf-cache-status
HIT
age
47260
content-encoding
gzip
x-content-type-options
nosniff
date
Sun, 06 Sep 2026 19:15:28 GMT
content-type
text/css
last-modified
Tue, 30 Sep 2025 02:10:15 GMT
strict-transport-security
max-age=31536000; includeSubDomains; preload
cache-control
max-age=86400
cross-origin-resource-policy
cross-origin
x-ms-request-id
0b9da502-801e-00f8-77d9-dc5897000000
cf-ray
a36fcd79b9a4d2c3-FRA
access-control-allow-origin
*
x-ms-blob-type
BlockBlob
server
cloudflare
GET
H3
200
abctelevision.js Show response
tru.am/scripts/custom/
1 KB
1 KB
267ms
135ms
Script
application/javascript
104.26.3.116
Cloudflare
General
Full URL
https://tru.am/scripts/custom/abctelevision.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.26.3.116 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
6cf55158477e6d82805e2299417765a85e22050b84bd77304beae71b7117dd98
Security Headers
Name Value
Strict-Transport-Security max-age=15552000; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
x-goog-hash
crc32c=/79rFA==, md5=RXJ4aPmzAL+eRtL4wJ1KXA==
cf-cache-status
HIT
etag
W/"45727868f9b300bf9e46d2f8c09d4a5c"
age
485327
content-encoding
br
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=Aezex9je2yp8xFTEEC3fFxeXtwn%2FRam2SouO6L12LxeIyQ4rQyczK3Hw9d2kx4JyEsqH2bCI9y%2B424GBrpU76WXO%2BYAj%2Bw0OjjL39JJ%2Fn7mtu7U3%2FkOQOA%3D%3D"}]}
x-content-type-options
nosniff
x-goog-stored-content-encoding
identity
expires
Wed, 01 Sep 2027 04:26:41 GMT
alt-svc
h3=":443"; ma=86400
x-goog-stored-content-length
1290
server-timing
cfExtPri
date
Sun, 06 Sep 2026 19:15:29 GMT
content-type
application/javascript
last-modified
Thu, 20 Jan 2022 17:08:22 GMT
vary
accept-encoding
priority
u=3,i=?0
x-guploader-uploadid
AHVrFxPQMOAX8cHKBulrDPdDQ586vJDH_o2jG7evAdxqgPK1HhTVgvA3CwSxHhcGR-OmYBa-
strict-transport-security
max-age=15552000; includeSubDomains; preload
cache-control
public, max-age=31536000
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
x-goog-storage-class
REGIONAL
cf-ray
a36fcd7aeff4d3b4-FRA
x-goog-generation
1642698502288915
server
cloudflare
GET
H2
200
ot_guard_logo.svg Show response
cdn.cookielaw.org/logos/static/
497 B
512 B
131ms
130ms
Fetch
image/svg+xml
104.18.87.42
Cloudflare
General
Full URL
https://cdn.cookielaw.org/logos/static/ot_guard_logo.svg
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.18.87.42 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
691dcdb24853a0f5ce4e6597e5713dea66799b57ffe2c2a10f28f98e0b569b19
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-md5
tXyZydHjxQshFMbbBT1/8A==
access-control-expose-headers
x-ms-request-id,Server,x-ms-version,Content-Type,ETag,Last-Modified,Content-MD5,x-ms-lease-status,x-ms-blob-type,Content-Length,Date,Transfer-Encoding
x-ms-version
2009-09-19
x-ms-lease-status
unlocked
cf-cache-status
HIT
age
67570
content-encoding
gzip
x-content-type-options
nosniff
date
Sun, 06 Sep 2026 19:15:29 GMT
content-type
image/svg+xml
last-modified
Tue, 01 Sep 2026 09:27:45 GMT
strict-transport-security
max-age=31536000; includeSubDomains; preload
cache-control
max-age=86400
cross-origin-resource-policy
cross-origin
x-ms-request-id
60b2b909-201e-0039-4b72-3ad32e000000
cf-ray
a36fcd7abd35d2c3-FRA
access-control-allow-origin
*
x-ms-blob-type
BlockBlob
server
cloudflare
GET
H2
200
ot_company_logo.png
cdn.cookielaw.org/logos/static/
19 KB
19 KB
131ms
130ms
Image
image/png
104.18.87.42
Cloudflare
General
Full URL
https://cdn.cookielaw.org/logos/static/ot_company_logo.png
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.18.87.42 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
97722715f92bfef1cccdf80f1dcee232f79e48a4b5612305ca2b864c352f0274
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-md5
QHB228W/DDZrpAols8WCfg==
access-control-expose-headers
x-ms-request-id,Server,x-ms-version,Content-Type,ETag,Last-Modified,Content-MD5,x-ms-lease-status,x-ms-blob-type,Content-Length,Date,Transfer-Encoding
x-ms-version
2009-09-19
x-ms-lease-status
unlocked
etag
0x8DF080B48A0E876
age
43205
cf-cache-status
HIT
x-content-type-options
nosniff
date
Sun, 06 Sep 2026 19:15:29 GMT
content-type
image/png
last-modified
Tue, 01 Sep 2026 09:27:46 GMT
strict-transport-security
max-age=31536000; includeSubDomains; preload
cache-control
max-age=86400
cross-origin-resource-policy
cross-origin
x-ms-request-id
604c23a8-401e-0088-4958-3a2b53000000
cf-ray
a36fcd7acb0ed390-FRA
accept-ranges
bytes
access-control-allow-origin
*
content-length
19373
x-ms-blob-type
BlockBlob
server
cloudflare
GET
H2
200
powered_by_logo.svg
cdn.cookielaw.org/logos/static/
5 KB
3 KB
126ms
125ms
Image
image/svg+xml
104.18.87.42
Cloudflare
General
Full URL
https://cdn.cookielaw.org/logos/static/powered_by_logo.svg
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.18.87.42 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
cddd450a33be5e50d6f27aea78d2e278beae2762678b22fc2dcee8de29cbc0be
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-md5
yMeilKp6reuDTG1eNiffRg==
access-control-expose-headers
x-ms-request-id,Server,x-ms-version,Content-Type,ETag,Last-Modified,Content-MD5,x-ms-lease-status,x-ms-blob-type,Content-Length,Date,Transfer-Encoding
x-ms-version
2009-09-19
x-ms-lease-status
unlocked
cf-cache-status
HIT
age
51607
content-encoding
gzip
x-content-type-options
nosniff
date
Sun, 06 Sep 2026 19:15:29 GMT
content-type
image/svg+xml
last-modified
Tue, 01 Sep 2026 09:27:46 GMT
strict-transport-security
max-age=31536000; includeSubDomains; preload
cache-control
max-age=86400
cross-origin-resource-policy
cross-origin
x-ms-request-id
24ac4356-601e-0071-5052-3ae1b3000000
cf-ray
a36fcd7acb16d390-FRA
access-control-allow-origin
*
x-ms-blob-type
BlockBlob
server
cloudflare
GET
DATA
200
OK
truncated
/
42 B
0
Image
image/gif

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/gif
GET

18509950_1280X720-ABC7-LOS-ANGELES.jpg
cdn.abcotvs.com/dip/images/
0
0


GET
H3
200
ta-pagesocial-sdk.js Show response
tru.am/scripts/
27 KB
11 KB
132ms
132ms
Script
text/javascript
104.26.3.116
Cloudflare
General
Full URL
https://tru.am/scripts/ta-pagesocial-sdk.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.26.3.116 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
7a20b371f96093be0c049b07134deb9bec533817ce791e865aaab7b60dfe4beb
Security Headers
Name Value
Strict-Transport-Security max-age=15552000; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
3
x-goog-hash
crc32c=TsbXyg==, md5=KSXI2pDR0p94mfpSYp/jfQ==
cf-cache-status
HIT
etag
W/"2925c8da90d1d29f7899fa52629fe37d"
age
228650
content-encoding
br
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=qgs%2BTqU5okArWeGtWpcCGXJiT8v1R6c9eqhSpV3%2Bq%2BS7bw8Bp7w7myquuhcDHdQwf8dU84gGmx8pXa4Rk1gP%2BhEoHkJ%2B18zrKVUbJDDBPU2m%2Bcg%2FWeb16g%3D%3D"}]}
x-content-type-options
nosniff
x-goog-stored-content-encoding
identity
expires
Fri, 04 Sep 2026 03:44:48 GMT
alt-svc
h3=":443"; ma=86400
x-goog-stored-content-length
27860
server-timing
cfExtPri
date
Sun, 06 Sep 2026 19:15:29 GMT
content-type
text/javascript
last-modified
Thu, 21 Jul 2022 07:45:14 GMT
vary
accept-encoding
priority
u=3,i=?0
x-guploader-uploadid
AKhXX7JkgLtV2Ihq6M4FMezgyPtopecGjLIpiVY5gdeNF2djf2wnHlUfniAKcehkpr62Jv8
strict-transport-security
max-age=15552000; includeSubDomains; preload
cache-control
max-age=2419200
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
x-goog-storage-class
REGIONAL
cf-ray
a36fcd7bc805d3b4-FRA
x-goog-generation
1658389514760491
server
cloudflare
GET
H2
200
ping
ping.chartbeat.net/
43 B
201 B
588ms
190ms
Image
image/gif
3.221.141.84
Amazon.com
General
Full URL
https://ping.chartbeat.net/ping?h=abc7.com&p=%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F&u=9bQN7CvU_-YCS53kA&d=abc7.com&g=23214&g0=No%20Section&g1=ABC7.COM%20STAFF&g7=1788359393000&n=1&f=00001&c=0&x=0&m=0&y=3345&o=1600&w=1200&j=45&R=1&W=0&I=0&E=0&e=0&r=&PA=https%3A%2F%2Fabc7.com%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F&b=1990&t=BlccMaBy-WlwBFGG2FBnUk3WmSeKK&V=152&i=3.4-magnitude%20earthquake%20hits%20Ontario%20area%2C%20shaking%20felt%20across%20San%20Bernardino%20County%2C%20USGS%20says&tz=-180&sn=1&sv=BpY6fNCXsoJQBnNB2kDkdAbtiBDis&sr=external&sd=1&im=067b0fff&_
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.221.141.84 Ashburn, United States, ASN14618 (AMAZON-AES - Amazon.com, Inc., US),
Reverse DNS
ec2-3-221-141-84.compute-1.amazonaws.com
Software
/
Resource Hash
cf4724b2f736ed1a0ae6bc28f1ead963d9cd2c1fd87b6ef32e7799fc1c5c8bda

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

expires
0
cache-control
no-cache, no-store, must-revalidate
content-length
43
date
Sun, 06 Sep 2026 19:15:29 GMT
pragma
no-cache
content-type
image/gif
cross-origin-resource-policy
cross-origin
GET
H2
200
chartbeat_mab.js Show response
static.chartbeat.com/js/
24 KB
10 KB
124ms
123ms
Script
application/x-javascript
18.245.63.132
Amazon.com
General
Full URL
https://static.chartbeat.com/js/chartbeat_mab.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
18.245.63.132 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-18-245-63-132.fra60.r.cloudfront.net
Software
openresty /
Resource Hash
ff324391dadd9368323fc2bbd7d5e235bd12f864f35e0310f586538ca119d4ab

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=86400
content-encoding
gzip
etag
W/"68116b61-5f1c"
age
53702
cross-origin-resource-policy
cross-origin
via
1.1 2b92d172bc628dd9c34a8c262218ac02.cloudfront.net (CloudFront)
expires
Mon, 07 Sep 2026 04:20:27 GMT
x-cache
Hit from cloudfront
x-amz-cf-id
W2b0L7PbSkyXdiGn0JdvFA7t8AfkYPFJMDPYFvWjWyb-sDKvFG7_wQ==
date
Sun, 06 Sep 2026 04:20:27 GMT
content-type
application/x-javascript
last-modified
Wed, 30 Apr 2025 00:14:25 GMT
server
openresty
x-amz-cf-pop
FRA60-P5
vary
Accept-Encoding
GET

26.svg
cdn.abcotvs.net/abcotv/assets/news/global/images/weather/dark24/
0
0


GET
H2
200
gpt.js Show response
www.googletagservices.com/tag/js/
127 KB
38 KB
369ms
135ms
Script
text/javascript
142.251.14.155
Google LLC
General
Full URL
https://www.googletagservices.com/tag/js/gpt.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.14.155 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f155.1e100.net
Software
cafe /
Resource Hash
abb8523eff07c607e2b399c55093e343859bf578d6ef42114ec1f23f4ac11d22
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
etag
553 / 20702 / m202609010101 / config-hash: 1310708616991806363
x-content-type-options
nosniff
expires
Sun, 06 Sep 2026 19:15:29 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
date
Sun, 06 Sep 2026 19:15:29 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-disposition
attachment; filename="f.txt"
cache-control
private, max-age=900, stale-while-revalidate=3600
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
content-length
38679
x-xss-protection
0
server
cafe
GET
H2
200
DATG-OTV.KABC.WEB Show response
login.disney.com/dev/oidcConfig/
418 B
670 B
384ms
121ms
Fetch
application/json
3.161.82.34
Amazon.com
General
Full URL
https://login.disney.com/dev/oidcConfig/DATG-OTV.KABC.WEB
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.34 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-34.fra56.r.cloudfront.net
Software
/
Resource Hash
d130ac282bf9ef1214b7d2b21b8f76b8303bf0517431eaa93959c16c0e0850d9

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
addacaf1eb22f0280bc0e626c63923f1
cache-control
public, s-maxage=900, max-age=0, must-revalidate, stale-while-revalidate=60, stale-if-error=900
content-encoding
gzip
age
671
x-bamtech-region
eu-central-1
via
1.1 9c8021538470ab47dffa34921d0b4aca.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
x-amz-cf-id
vzXBwe0P5i7AWkzhIUUZniTNBly3Onjw2O0CdFyqleLoOVcJO0sbLA==
date
Sun, 06 Sep 2026 19:04:18 GMT
content-type
application/json
vary
Accept-Encoding,RSC
x-amz-cf-pop
FRA56-P10
POST
H3
204
beacon
beacon.tru.am/
0
0
347ms
224ms
Fetch
104.26.2.116
Cloudflare
General
Full URL
https://beacon.tru.am/beacon
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.26.2.116 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
Security Headers
Name Value
Strict-Transport-Security max-age=15552000; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
Content-Type
application/x-www-form-urlencoded;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

surrogate-control
no-store
access-control-max-age
86400
cf-cache-status
DYNAMIC
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=zRWC3ulaA3%2F7zwrhxtGrNAid7eBdLWN6D90pKlDSxiMiSdmAMZHQaWGs9VjJt10fbNyeSjyDpdaXfpAJ5vXkn7MCR72pdf6cb3QoiMQHNeRuYkg5iUdb4FArwkmXb2s%3D"}]}
x-content-type-options
nosniff
expires
Thu, 01 Jan 1970 00:00:00 UTC
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Sun, 06 Sep 2026 19:15:29 GMT
priority
u=1,i
strict-transport-security
max-age=15552000; includeSubDomains; preload
cache-control
no-store, no-cache, must-revalidate, proxy-revalidate
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
pragma
no-cache
via
1.1 google
cf-ray
a36fcd7d5d2abb77-FRA
access-control-allow-origin
*
server
cloudflare
GET
H2
200
/ Show response
mab.chartbeat.com/mab_strategy/headline_testing/get_strategy/
246 B
603 B
464ms
200ms
XHR
application/json
151.101.66.202
Fastly
General
Full URL
https://mab.chartbeat.com/mab_strategy/headline_testing/get_strategy/?host=abc7.com&domain=abc7.com&path=%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
151.101.66.202 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
/
Resource Hash
f8052bd3e2ccf571f4fa26961426db133152db96905f4ea72db28ca1d91bf566

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
age
0
expires
Fri, 04 Sep 2026 19:15:29 GMT
x-cache
MISS
date
Sun, 06 Sep 2026 19:15:29 GMT
content-type
application/json
x-served-by
cache-lon4224-LON
x-cache-hits
0
vary
Origin, Access-Control-Request-Headers, Access-Control-Request-Method, Accept-Encoding, Accept-Encoding
cache-control
no-store, no-cache, must-revalidate, max-age=0, s-maxage=0
x-timer
S1788722130.684187,VS0,VE82
cross-origin-resource-policy
cross-origin
via
1.1 varnish (Varnish/6.6), 1.1 varnish
accept-ranges
bytes
access-control-allow-origin
*
content-length
238
GET
H2
200
/ Show response
mab.chartbeat.com/mab_strategy/headline_testing/get_strategy/
246 B
313 B
582ms
118ms
XHR
application/json
151.101.66.202
Fastly
General
Full URL
https://mab.chartbeat.com/mab_strategy/headline_testing/get_strategy/?host=abc7.com&domain=abc7.com&path=%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
151.101.66.202 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
/
Resource Hash
f8052bd3e2ccf571f4fa26961426db133152db96905f4ea72db28ca1d91bf566

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
age
0
expires
Fri, 04 Sep 2026 19:15:29 GMT
x-cache
HIT
date
Sun, 06 Sep 2026 19:15:29 GMT
content-type
application/json
x-served-by
cache-lon4224-LON
x-cache-hits
1
vary
Origin, Access-Control-Request-Headers, Access-Control-Request-Method, Accept-Encoding, Accept-Encoding
cache-control
no-store, no-cache, must-revalidate, max-age=0, s-maxage=0
x-timer
S1788722130.884536,VS0,VE1
cross-origin-resource-policy
cross-origin
via
1.1 varnish (Varnish/6.6), 1.1 varnish
accept-ranges
bytes
access-control-allow-origin
*
content-length
238
GET
H2
200
/ Show response
mab.chartbeat.com/mab_strategy/headline_testing/get_strategy/
246 B
326 B
700ms
117ms
XHR
application/json
151.101.66.202
Fastly
General
Full URL
https://mab.chartbeat.com/mab_strategy/headline_testing/get_strategy/?host=abc7.com&domain=abc7.com&path=%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
151.101.66.202 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
/
Resource Hash
f8052bd3e2ccf571f4fa26961426db133152db96905f4ea72db28ca1d91bf566

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
age
0
expires
Fri, 04 Sep 2026 19:15:29 GMT
x-cache
HIT
date
Sun, 06 Sep 2026 19:15:30 GMT
content-type
application/json
x-served-by
cache-lon4224-LON
x-cache-hits
2
vary
Origin, Access-Control-Request-Headers, Access-Control-Request-Method, Accept-Encoding, Accept-Encoding
cache-control
no-store, no-cache, must-revalidate, max-age=0, s-maxage=0
x-timer
S1788722130.003157,VS0,VE0
cross-origin-resource-policy
cross-origin
via
1.1 varnish (Varnish/6.6), 1.1 varnish
accept-ranges
bytes
access-control-allow-origin
*
content-length
238
GET
H2
200
tr5
cdn.taboola.com/libtrc/
3 B
96 B
119ms
118ms
Image
text/html
151.101.193.44
Fastly
General
Full URL
https://cdn.taboola.com/libtrc/tr5?type=loaderpixel&publisher=abcotvweb-network&bundle=default
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
Varnish /
Resource Hash
2e34af284c28bf285781a36241b6e00ec74c81e6ae6858d52bdede5ebf7e37c1

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-fastly-object-storage
false
cache-control
private,max-age=14400
retry-after
0
x-timer
S1788722130.542352,VS0,VE0
via
1.1 varnish
accept-ranges
bytes
access-control-allow-origin
*
x-cache
HIT
content-length
3
date
Sun, 06 Sep 2026 19:15:29 GMT
content-type
text/html
x-served-by
cache-lon4258-LON
server
Varnish
x-cache-hits
0
GET
H2
200
sync Show response
gum.criteo.com/
Redirect Chain
  • https://gum.criteo.com/sync?c=72&r=2&j=TRC.getRTUS
  • https://gum.criteo.com/sync?s=1&c=72&r=2&j=TRC.getRTUS
136 B
754 B
124ms
124ms
Script
text/javascript
178.250.1.12
ASN-CRITEO-EUROPE...
General
Full URL
https://gum.criteo.com/sync?s=1&c=72&r=2&j=TRC.getRTUS
Protocol
H2
Server
178.250.1.12 , France, ASN44788 (ASN-CRITEO-EUROPE Criteo Technology SAS, FR),
Reverse DNS
Software
Kestrel /
Resource Hash
c55e9fe252416ab7fcac869fd90d0845655f88eecf190ff94e5e68a5cbb25e0d
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; preload;

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
Referer
https://abc7.com/

Response headers

strict-transport-security
max-age=31536000; preload;
cache-control
private, no-cache, max-age=0, must-revalidate
content-encoding
gzip
server-processing-duration-in-ticks
1309093
date
Sun, 06 Sep 2026 19:15:29 GMT
content-type
text/javascript; charset=utf-8
vary
Accept-Encoding
server
Kestrel

Redirect headers

strict-transport-security
max-age=31536000; preload;
cache-control
private, no-cache, max-age=0, must-revalidate
location
/sync?s=1&c=72&r=2&j=TRC.getRTUS
content-length
0
date
Sun, 06 Sep 2026 19:15:29 GMT
server
Kestrel
server-processing-duration-in-ticks
217780
POST
H2
200
json Show response
trc.taboola.com/abcotvweb-abc7la/trc/3/
147 KB
48 KB
597ms
591ms
Fetch
application/javascript
151.101.193.44
Fastly
General
Full URL
https://trc.taboola.com/abcotvweb-abc7la/trc/3/json?llvl=2&tim=22%3A15%3A29.500&lti=default&pubit=n&t=1&data=%7B%22cmps%22%3A0%2C%22gpp%22%3A%22DBABLA~BVQqAAAAAAJY.QA%22%2C%22gpp_sid%22%3A%227%22%2C%22id%22%3A%2254667%22%2C%22sd%22%3A%22%22%2C%22ui%22%3A%22%22%2C%22ii%22%3A%22%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%22%2C%22it%22%3A%22text%22%2C%22vi%22%3A1788722129500%2C%22cv%22%3A%2220260906-3-RELEASE%22%2C%22uiv%22%3A%22default%22%2C%22u%22%3A%22https%3A%2F%2Fabc7.com%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F%22%2C%22qs%22%3A%22%22%2C%22bv%22%3A%220%22%2C%22btv%22%3A%220%22%2C%22ul%22%3A%5B%22he-IL%22%5D%2C%22cos%22%3A%224g%22%2C%22bu%22%3A%22https%3A%2F%2Fabc7.com%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F%22%2C%22vpi%22%3A%22%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%22%2C%22bad%22%3A-1%2C%22sw%22%3A1600%2C%22sh%22%3A1200%2C%22bw%22%3A1600%2C%22bh%22%3A1200%2C%22dw%22%3A1600%2C%22dh%22%3A3345%2C%22sde%22%3A%221.000%22%2C%22lt%22%3A%22default%22%2C%22nsid%22%3A%22abcotvweb-network%22%2C%22r%22%3A%5B%7B%22li%22%3A%22rbox-t2m%22%2C%22uip%22%3A%22Below%20Article%20Thumbnails%22%2C%22orig_uip%22%3A%22Below%20Article%20Thumbnails%22%2C%22s%22%3A9%2C%22uim%22%3A%22thumbnails-a%3Apub%3Dabcotvweb-network%3Aabp%3D0%22%2C%22cd%22%3A1932.14%2C%22mw%22%3A718%7D%5D%2C%22uad%22%3A%7B%22mobile%22%3Afalse%2C%22model%22%3A%22%22%2C%22platform%22%3A%22Linux%22%2C%22platformVersion%22%3A%22%22%2C%22uaFullVersion%22%3A%22152.0.7977.82%22%7D%2C%22cacheKey%22%3A%22text%3D%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2CBelow%20Article%20Thumbnails%3Dthumbnails-a%3Apub%3Dabcotvweb-network%3Aabp%3D0%22%2C%22_cn%22%3A%22tions_1%22%2C%22lbt%22%3A1788686697209%2C%22wc%22%3Atrue%2C%22bs%22%3A%7B%22at%22%3A1%2C%22zm%22%3A0%2C%22ls%22%3Atrue%2C%22lm%22%3A-1%2C%22lt%22%3A-1%7D%7D
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
nginx /
Resource Hash
a9596e774c890bb91b4a2ddb4e42c17274c0ad22646039da5eb5c75665586ff0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
Content-Type
text/plain
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-cache
MISS
p3p
policyref="http://trc.taboola.com/p3p.xml", CP="NOI DSP COR LAW NID CURa ADMa DEVa PSAa PSDa OUR BUS IND UNI COM NAV INT DEM"
x-log-content-encoding
gzip
date
Sun, 06 Sep 2026 19:15:30 GMT
content-type
application/javascript; charset=utf-8
x-served-by
cache-lon4258-LON
x-cache-hits
0
vary
Accept-Encoding
x-fastly-to-nlb-rtt
71821
x-timer
S1788722130.568770,VS0,VE474
x-vcl-time-ms
474
access-control-allow-credentials
true
via
1.1 varnish
cpu
0.45895833333333336
accept-ranges
bytes
access-control-allow-origin
https://abc7.com
x-service-version
v1
server
nginx
GET
H2
200
ee00cbb1c51732236f4cb00852a1104f.js Show response
dcf.espn.com/TWDC-DTCI/prod/code/
1 KB
1 KB
134ms
132ms
Script
application/javascript
3.124.173.63
Amazon.com
General
Full URL
https://dcf.espn.com/TWDC-DTCI/prod/code/ee00cbb1c51732236f4cb00852a1104f.js?conditionId0=4871166
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
3.124.173.63 Frankfurt am Main, Germany, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-3-124-173-63.eu-central-1.compute.amazonaws.com
Software
CloudFront /
Resource Hash
09aa197b780bfe7b955974d6d0445d27e123088102766ce969315233d7379aad

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
x-amz-version-id
sboXdaYeOAXO_6IsXfODlX.DNsz7QwmP
etag
W/"f844dc74d8fc792a359204fe34a5acf3"
age
13633251
alt-svc
h3=":443"; ma=86400
x-cache
Hit from cloudfront
x-amz-cf-id
E3ShecubasYXyn8nLa9MAK33LnulcYp2CKKROwR6WLh4-1jObThrbA==
date
Sun, 06 Sep 2026 19:15:29 GMT
content-type
application/javascript; charset=utf-8
vary
Accept-Encoding, Origin
last-modified
Tue, 31 Mar 2026 11:13:51 GMT
x-amz-replication-status
COMPLETED
cache-control
max-age=315360000
via
1.1 93efd892a8e99dc59164afbee331cd56.cloudfront.net (CloudFront)
x-amz-cf-pop
FRA56-P7
server
CloudFront
x-amz-server-side-encryption
AES256
GET
H2
200
457b661e42f01838fade625430c8f13d.js Show response
dcf.espn.com/TWDC-DTCI/prod/code/
5 KB
2 KB
135ms
134ms
Script
application/javascript
3.124.173.63
Amazon.com
General
Full URL
https://dcf.espn.com/TWDC-DTCI/prod/code/457b661e42f01838fade625430c8f13d.js?conditionId0=4907063
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
3.124.173.63 Frankfurt am Main, Germany, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-3-124-173-63.eu-central-1.compute.amazonaws.com
Software
CloudFront /
Resource Hash
def56de207b98cd5464c1b9e069c49faaa293ab6797216e5202c5ff02627f84e

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-amz-version-id
9.FddMxz_NQgDxyig9jVy8AkdBoGLmQj
etag
W/"f7c8dbddb7f1e9b59544910dc2198908"
age
12963940
alt-svc
h3=":443"; ma=86400
x-cache
Hit from cloudfront
x-amz-cf-id
-yvBwR87IoCXsVYTLN2xSUs6TSkl7ffTr8nvWCmk7ha-6sNmZ7MFSQ==
date
Sun, 06 Sep 2026 19:15:29 GMT
content-type
application/javascript; charset=utf-8
vary
Accept-Encoding, Origin
last-modified
Thu, 09 Apr 2026 18:09:32 GMT
x-amz-replication-status
PENDING
cache-control
max-age=315360000
via
1.1 4dd80d99fd5d0f6baaaf5179cd921f72.cloudfront.net (CloudFront)
x-amz-cf-pop
FRA56-P7
server
CloudFront
x-amz-server-side-encryption
AES256
GET
H2
200
e5bfce2f989584b09f15a19f53be8dfd.js Show response
dcf.espn.com/TWDC-DTCI/prod/code/
436 KB
119 KB
193ms
192ms
Script
application/javascript
3.124.173.63
Amazon.com
General
Full URL
https://dcf.espn.com/TWDC-DTCI/prod/code/e5bfce2f989584b09f15a19f53be8dfd.js?conditionId0=4905161
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
3.124.173.63 Frankfurt am Main, Germany, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-3-124-173-63.eu-central-1.compute.amazonaws.com
Software
CloudFront /
Resource Hash
b095d8aa7676ad0e462f2918b07cab18d7c2f53d4548f15f9b736be41f1a4949

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-amz-version-id
BTbd9.tJMmar1cWnP6VePAgxI5p5SFB0
etag
W/"4f43190a146044c4935bc7b4dd58f980"
age
2875616
alt-svc
h3=":443"; ma=86400
x-cache
Hit from cloudfront
x-amz-cf-id
e5elcLVFNAHSV3FoH8jc66J5bOGHA6JUsRuAowhULGdg4Oa2jA5HzA==
date
Sun, 06 Sep 2026 19:15:29 GMT
content-type
application/javascript; charset=utf-8
vary
Accept-Encoding, Origin
last-modified
Tue, 04 Aug 2026 12:28:06 GMT
x-amz-replication-status
COMPLETED
cache-control
max-age=315360000
via
1.1 6f32a39163a1e36ace7a71a85e2d2884.cloudfront.net (CloudFront)
x-amz-cf-pop
FRA56-P7
server
CloudFront
x-amz-server-side-encryption
AES256
GET
H2
200
a4f1b07b4c52d912c0dcd2cb98943681.js Show response
dcf.espn.com/TWDC-DTCI/prod/code/
178 KB
55 KB
252ms
251ms
Script
application/javascript
3.124.173.63
Amazon.com
General
Full URL
https://dcf.espn.com/TWDC-DTCI/prod/code/a4f1b07b4c52d912c0dcd2cb98943681.js?conditionId0=4901551
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
3.124.173.63 Frankfurt am Main, Germany, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-3-124-173-63.eu-central-1.compute.amazonaws.com
Software
CloudFront /
Resource Hash
154d36cd432edc20ff48caa8fabff9bedec07cfb26e9b6ccabac50da458fdb8d

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
x-amz-version-id
g.N306pFkGckLkYrNkS6mHBtrVwUM0L9
etag
W/"2074fd9c5f3f071cad212abf817e8786"
age
275645
alt-svc
h3=":443"; ma=86400
x-cache
Hit from cloudfront
x-amz-cf-id
lExkBWGkvcBk3-DtcaUteIpocCBvNxGlnQz3GZ0fW907KUg4ww_OTg==
date
Sun, 06 Sep 2026 19:15:29 GMT
content-type
application/javascript; charset=utf-8
vary
Accept-Encoding, Origin
last-modified
Thu, 03 Sep 2026 14:41:22 GMT
x-amz-replication-status
PENDING
cache-control
max-age=315360000
via
1.1 d76db2cbee553c8bb2de7fd88a960646.cloudfront.net (CloudFront)
x-amz-cf-pop
FRA56-P7
server
CloudFront
x-amz-server-side-encryption
AES256
GET
H2
200
d0de89e5b157554f7b7e9a623efd74f2.js Show response
dcf.espn.com/TWDC-DTCI/prod/code/
2 KB
1 KB
198ms
197ms
Script
application/javascript
3.124.173.63
Amazon.com
General
Full URL
https://dcf.espn.com/TWDC-DTCI/prod/code/d0de89e5b157554f7b7e9a623efd74f2.js?conditionId0=4958026
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
3.124.173.63 Frankfurt am Main, Germany, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-3-124-173-63.eu-central-1.compute.amazonaws.com
Software
CloudFront /
Resource Hash
c721d9db507e58644f1820fb6260a9760f3f8d1e25f68c7d06981edad5f52ac8

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-amz-version-id
B7wrIqtChLVVBzPZRXq7vf2KlhU4bOyt
etag
W/"39fe38f116bbab499584d8c11b6ed75f"
age
25749126
alt-svc
h3=":443"; ma=86400
x-cache
Hit from cloudfront
x-amz-cf-id
EVqU1Re3AlLeoHIZzninUsk_OpybKFkZ6ljA5GOSEfhLEfDe-fww3A==
date
Sun, 06 Sep 2026 19:15:29 GMT
content-type
application/javascript; charset=utf-8
vary
accept-encoding, Origin
last-modified
Thu, 11 Sep 2025 17:35:33 GMT
x-amz-replication-status
COMPLETED
cache-control
max-age=315360000
via
1.1 fa87f2173bfe5d35fd73cec71ab12a32.cloudfront.net (CloudFront)
x-amz-cf-pop
FRA56-P7
server
CloudFront
x-amz-server-side-encryption
AES256
GET
H2
200
f7f6f3df36dffde5c1c466d6e298fa26.js Show response
dcf.espn.com/TWDC-DTCI/prod/code/
17 KB
5 KB
253ms
253ms
Script
application/javascript
3.124.173.63
Amazon.com
General
Full URL
https://dcf.espn.com/TWDC-DTCI/prod/code/f7f6f3df36dffde5c1c466d6e298fa26.js?conditionId0=4901551
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
3.124.173.63 Frankfurt am Main, Germany, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-3-124-173-63.eu-central-1.compute.amazonaws.com
Software
CloudFront /
Resource Hash
70775b7a1f1ed1855aa1c4d3877c9f6b394f2f38154cb4a02eed5511366e63f3

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
x-amz-version-id
CcQSNGjrpnKg0SdRZopi3CSn738gSnrU
etag
W/"4c702aedad34785c1cd6f8818c8e11d0"
age
9826534
alt-svc
h3=":443"; ma=86400
x-cache
Hit from cloudfront
x-amz-cf-id
CEL96X53Pho97U-VRyVhqRSEWDcs0ZU5Px68ToRuqnLTjxO5--3xXQ==
date
Sun, 06 Sep 2026 19:15:29 GMT
content-type
application/javascript; charset=utf-8
vary
Accept-Encoding, Origin
last-modified
Thu, 26 Feb 2026 17:30:13 GMT
x-amz-replication-status
COMPLETED
cache-control
max-age=315360000
via
1.1 9b7b71910b45e646f6476bbd270127a4.cloudfront.net (CloudFront)
x-amz-cf-pop
FRA56-P7
server
CloudFront
x-amz-server-side-encryption
AES256
GET
H2
200
a5ce752ca1d0c0f14a1559bc2835e5b5.js Show response
dcf.espn.com/TWDC-DTCI/prod/code/
12 KB
3 KB
328ms
327ms
Script
application/javascript
3.124.173.63
Amazon.com
General
Full URL
https://dcf.espn.com/TWDC-DTCI/prod/code/a5ce752ca1d0c0f14a1559bc2835e5b5.js?conditionId0=4905161
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
3.124.173.63 Frankfurt am Main, Germany, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-3-124-173-63.eu-central-1.compute.amazonaws.com
Software
CloudFront /
Resource Hash
96cbb5cad667964e352513dac6ad1eb26f45de4c23a8d24a60221cea259b7a25

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
x-amz-version-id
5wJsYNng9ukkIx2kq6EO17OucOBuQlhc
etag
W/"9fe4703daafa861676f079ff1c816957"
age
2346056
alt-svc
h3=":443"; ma=86400
x-cache
Hit from cloudfront
x-amz-cf-id
Rtn36b2kcfAta-IKKvEoGRTqMT4cGUewzk5vko-uhaNKVmxaScP0xQ==
date
Sun, 06 Sep 2026 19:15:29 GMT
content-type
application/javascript; charset=utf-8
vary
Accept-Encoding, Origin
last-modified
Mon, 10 Aug 2026 15:34:26 GMT
x-amz-replication-status
PENDING
cache-control
max-age=315360000
via
1.1 8dc3ccc34d68ee81173fff2a80f72bde.cloudfront.net (CloudFront)
x-amz-cf-pop
FRA56-P7
server
CloudFront
x-amz-server-side-encryption
AES256
OPTIONS
H2
204
graphql
disney-entertainment.api.edge.bamgrid.com/graph/v1/device/ Frame
0
0
373ms
118ms
Preflight
18.239.105.88
Amazon.com
General
Full URL
https://disney-entertainment.api.edge.bamgrid.com/graph/v1/device/graphql
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
18.239.105.88 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-18-239-105-88.ams1.r.cloudfront.net
Software
/
Resource Hash

Request headers

Accept
*/*
Access-Control-Request-Headers
authorization,content-type,x-application-version,x-bamsdk-client-id,x-bamsdk-platform,x-bamsdk-platform-id,x-bamsdk-version,x-dss-edge-accept,x-request-id,x-request-yp-id
Access-Control-Request-Method
POST
Origin
https://abc7.com
Sec-Fetch-Mode
cors
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36

Response headers

access-control-allow-credentials
true
access-control-allow-headers
authorization,content-type,x-application-version,x-bamsdk-client-id,x-bamsdk-platform,x-bamsdk-platform-id,x-bamsdk-version,x-dss-edge-accept,x-request-id,x-request-yp-id
access-control-allow-methods
GET, POST, PUT, PATCH, DELETE, OPTIONS
access-control-allow-origin
https://abc7.com
access-control-expose-headers
x-request-id, x-bamtech-region, date
access-control-max-age
600
age
3248
cache-control
public, max-age=3600
date
Sun, 06 Sep 2026 18:21:21 GMT
vary
origin,access-control-request-headers
via
1.1 92cfe9224b3a51aff944c5d8ac7bf798.cloudfront.net (CloudFront)
x-amz-cf-id
NsHyhcd5yBKKXV9G84mEEqXIuEFu-z1L3b5bOOOyVO7h3P3EGPEnVA==
x-amz-cf-pop
AMS1-P3
x-bamtech-region
eu-central-1
x-cache
Hit from cloudfront
x-request-id
448237d4d8b068f4ca9a9ef8eb72ae75
POST
H2
200
graphql Show response
disney-entertainment.api.edge.bamgrid.com/graph/v1/device/
8 KB
6 KB
222ms
221ms
Fetch
application/json
18.239.105.88
Amazon.com
General
Full URL
https://disney-entertainment.api.edge.bamgrid.com/graph/v1/device/graphql
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
18.239.105.88 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-18-239-105-88.ams1.r.cloudfront.net
Software
/
Resource Hash
f21cb430d1f15822fa67a28b71ea1ca6d677546268726ee3121ca349c4fb8412

Request headers

x-application-version
1.3
x-request-id
f4171ee0-ed1a-4f43-a93b-5049fd9e566c
authorization
Bearer YWJjX25ld3NfbG9zX2FuZ2VsZXMmYnJvd3NlciYxLjAuMA.wUbhdlgLA6GYCUdfeeW9RtW1iwQkEOgch6LEKVL8K2Q
sec-ch-ua-platform
"Linux"
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
accept
application/json
content-type
application/json
Referer
https://abc7.com/
x-request-yp-id
624b805dafc5c73635b1a216
x-bamsdk-client-id
abc_news_los_angeles-d652ef7d
x-bamsdk-version
35.3
x-bamsdk-platform
javascript/linux/chrome
x-dss-edge-accept
vnd.dss.edge+json; version=2
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
x-bamsdk-platform-id
browser

Response headers

access-control-max-age
600
x-request-id
f4171ee0-ed1a-4f43-a93b-5049fd9e566c
access-control-expose-headers
x-request-id, x-bamtech-region, date
content-encoding
gzip
access-control-allow-methods
GET, POST, PUT, PATCH, DELETE, OPTIONS
x-cache
Miss from cloudfront
x-amz-cf-id
CysPrj9HpxWnAJqZpnkZm17b6yQ3iaE8EX2mUczQ2qYV3brN-XmT8g==
date
Sun, 06 Sep 2026 19:15:30 GMT
content-type
application/json
vary
origin, access-control-request-headers
cache-control
no-store
access-control-allow-credentials
true
x-bamtech-region
eu-central-1
via
1.1 92cfe9224b3a51aff944c5d8ac7bf798.cloudfront.net (CloudFront)
access-control-allow-origin
https://abc7.com
x-amz-cf-pop
AMS1-P3
GET
DATA
200
OK
truncated
/
73 B
73 B
Image
image/svg

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
38814c5240d913c5270db8b8c3eae9f192489b2d2752b63c30562c4287f70015

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/svg
GET

19779720_090226-kabc-ontario-quake-tn.jpg
cdn.abcotvs.com/dip/images/
0
0


GET
H2
200
graphql Show response
login.disney.com/api/
19 KB
3 KB
126ms
126ms
Fetch
application/json
3.161.82.34
Amazon.com
General
Full URL
https://login.disney.com/api/graphql?query=%0A++query+GetSiteConfig%28%24input%3A+GetSiteConfigInput%21%29+%7B%0A++++getSiteConfig%28input%3A+%24input%29+%7B%0A++++++compliance+%7B%0A++++++++ageBands%0A++++++++defaultAgeBand%0A++++++++defaultCountryCode%0A++++++%7D%0A++++++uiConfig%0A++++++newsletters+%7B%0A++++++++ADULT%0A++++++++TEEN%0A++++++++CHILD%0A++++++%7D%0A++++++displayName+%7B%0A++++++++enabled%0A++++++++suffixLength%0A++++++++display+%7B%0A++++++++++default+%7B%0A++++++++++++visible%0A++++++++++%7D%0A++++++++++create+%7B%0A++++++++++++visible%0A++++++++++%7D%0A++++++++++update+%7B%0A++++++++++++visible%0A++++++++++%7D%0A++++++++++login+%7B%0A++++++++++++visible%0A++++++++++%7D%0A++++++++%7D%0A++++++%7D%0A++++++legal+%7B%0A++++++++ADULT+%7B%0A++++++++++disclosures+%7B%0A++++++++++++canBeDeferred%0A++++++++++++content+%7B%0A++++++++++++++text%0A++++++++++++++links%0A++++++++++++%7D%0A++++++++++++disclosureCode%0A++++++++++++documents%0A++++++++++++requiresActiveConsent%0A++++++++++++requiresActiveReview%0A++++++++++++ruleType%0A++++++++++++sortingTag%0A++++++++++%7D%0A++++++++%7D%0A++++++++CHILD+%7B%0A++++++++++disclosures+%7B%0A++++++++++++canBeDeferred%0A++++++++++++content+%7B%0A++++++++++++++text%0A++++++++++++++links+%0A++++++++++++%7D%0A++++++++++++disclosureCode%0A++++++++++++documents%0A++++++++++++requiresActiveConsent%0A++++++++++++requiresActiveReview%0A++++++++++++ruleType%0A++++++++++++sortingTag%0A++++++++++%7D%0A++++++++%7D%0A++++++++TEEN+%7B%0A++++++++++disclosures+%7B%0A++++++++++++canBeDeferred%0A++++++++++++content+%7B%0A++++++++++++++text%0A++++++++++++++links%0A++++++++++++%7D%0A++++++++++++disclosureCode%0A++++++++++++documents%0A++++++++++++requiresActiveConsent%0A++++++++++++requiresActiveReview%0A++++++++++++ruleType%0A++++++++++++sortingTag%0A++++++++++%7D%0A++++++++%7D%0A++++++%7D%0A++++%7D%0A++%7D%0A&variables=%7B%22input%22%3A%7B%7D%7D
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.34 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-34.fra56.r.cloudfront.net
Software
/
Resource Hash
e08c21f77747ba50a2abfbe2178f71d95ac5b37a02f79dfb71461f0af662b13a

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
x-disney-identity-language-preference
en-US
x-disney-identity-client-id
DATG-OTV.KABC.WEB
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
content-type
application/json

Response headers

x-request-id
19166cb7d7c38a93e98821b5434ccd0a
access-control-max-age
600
access-control-expose-headers
x-request-id, x-bamtech-region, date
content-encoding
br
age
1279
access-control-allow-methods
GET, POST, PUT, PATCH, DELETE, OPTIONS
x-cache
Hit from cloudfront
x-amz-cf-id
cRHGe8_uEQL0PCGFATXHmyllpMQyPgAGQXHV4P0-aMITBJ_yROjAJA==
date
Sun, 06 Sep 2026 18:54:10 GMT
content-type
application/json
vary
origin,access-control-request-headers
cache-control
public, max-age=900, stale-while-revalidate=86400, stale-if-error=86400
apollo-trace-id
712a1608e6c2555862d6217c43f48717
access-control-allow-credentials
true
x-bamtech-region
eu-central-1
via
1.1 9c8021538470ab47dffa34921d0b4aca.cloudfront.net (CloudFront)
access-control-allow-origin
https://abc7.com
x-amz-cf-pop
FRA56-P10
OPTIONS
H2
204
graphql
login.disney.com/api/ Frame
0
0
124ms
124ms
Preflight
3.161.82.34
Amazon.com
General
Full URL
https://login.disney.com/api/graphql?query=%0A++query+GetSiteConfig%28%24input%3A+GetSiteConfigInput%21%29+%7B%0A++++getSiteConfig%28input%3A+%24input%29+%7B%0A++++++compliance+%7B%0A++++++++ageBands%0A++++++++defaultAgeBand%0A++++++++defaultCountryCode%0A++++++%7D%0A++++++uiConfig%0A++++++newsletters+%7B%0A++++++++ADULT%0A++++++++TEEN%0A++++++++CHILD%0A++++++%7D%0A++++++displayName+%7B%0A++++++++enabled%0A++++++++suffixLength%0A++++++++display+%7B%0A++++++++++default+%7B%0A++++++++++++visible%0A++++++++++%7D%0A++++++++++create+%7B%0A++++++++++++visible%0A++++++++++%7D%0A++++++++++update+%7B%0A++++++++++++visible%0A++++++++++%7D%0A++++++++++login+%7B%0A++++++++++++visible%0A++++++++++%7D%0A++++++++%7D%0A++++++%7D%0A++++++legal+%7B%0A++++++++ADULT+%7B%0A++++++++++disclosures+%7B%0A++++++++++++canBeDeferred%0A++++++++++++content+%7B%0A++++++++++++++text%0A++++++++++++++links%0A++++++++++++%7D%0A++++++++++++disclosureCode%0A++++++++++++documents%0A++++++++++++requiresActiveConsent%0A++++++++++++requiresActiveReview%0A++++++++++++ruleType%0A++++++++++++sortingTag%0A++++++++++%7D%0A++++++++%7D%0A++++++++CHILD+%7B%0A++++++++++disclosures+%7B%0A++++++++++++canBeDeferred%0A++++++++++++content+%7B%0A++++++++++++++text%0A++++++++++++++links+%0A++++++++++++%7D%0A++++++++++++disclosureCode%0A++++++++++++documents%0A++++++++++++requiresActiveConsent%0A++++++++++++requiresActiveReview%0A++++++++++++ruleType%0A++++++++++++sortingTag%0A++++++++++%7D%0A++++++++%7D%0A++++++++TEEN+%7B%0A++++++++++disclosures+%7B%0A++++++++++++canBeDeferred%0A++++++++++++content+%7B%0A++++++++++++++text%0A++++++++++++++links%0A++++++++++++%7D%0A++++++++++++disclosureCode%0A++++++++++++documents%0A++++++++++++requiresActiveConsent%0A++++++++++++requiresActiveReview%0A++++++++++++ruleType%0A++++++++++++sortingTag%0A++++++++++%7D%0A++++++++%7D%0A++++++%7D%0A++++%7D%0A++%7D%0A&variables=%7B%22input%22%3A%7B%7D%7D
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.34 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-34.fra56.r.cloudfront.net
Software
/
Resource Hash

Request headers

Accept
*/*
Access-Control-Request-Headers
content-type,x-disney-identity-client-id,x-disney-identity-language-preference
Access-Control-Request-Method
GET
Origin
https://abc7.com
Sec-Fetch-Mode
cors
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36

Response headers

access-control-allow-credentials
true
access-control-allow-headers
content-type,x-disney-identity-client-id,x-disney-identity-language-preference
access-control-allow-methods
GET, POST, PUT, PATCH, DELETE, OPTIONS
access-control-allow-origin
https://abc7.com
access-control-expose-headers
x-request-id, x-bamtech-region, date
access-control-max-age
600
age
1280
cache-control
public, max-age=3600
date
Sun, 06 Sep 2026 18:54:09 GMT
vary
origin,access-control-request-headers
via
1.1 9c8021538470ab47dffa34921d0b4aca.cloudfront.net (CloudFront)
x-amz-cf-id
RQDN08Qw6PW5D7Q28S0WtrfqGuh61vN4XQA9E5bl9HQzkYl6H2d0kA==
x-amz-cf-pop
FRA56-P10
x-bamtech-region
eu-central-1
x-cache
Hit from cloudfront
x-request-id
98df2d5ac6fa635a0c56c53557e1c164
GET
H3
200
pubads_impl.js Show response
securepubads.g.doubleclick.net/pagead/managed/js/gpt/m202609010101/
685 KB
211 KB
263ms
115ms
Script
text/javascript
142.250.154.154
Google LLC
General
Full URL
https://securepubads.g.doubleclick.net/pagead/managed/js/gpt/m202609010101/pubads_impl.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.250.154.154 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bt-in-f154.1e100.net
Software
cafe /
Resource Hash
4d064f15e95a797de35f666978f39e3c9c2c5a526cd09a0b8e2a53ec26c75557
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
etag
2254761434344483130
age
21189
x-content-type-options
nosniff
expires
Mon, 06 Sep 2027 13:22:20 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
date
Sun, 06 Sep 2026 13:22:20 GMT
content-disposition
attachment; filename="f.txt"
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
cache-control
public, immutable, max-age=31536000
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
content-length
215780
x-xss-protection
0
server
cafe
GET
H3
200
gpt
securepubads.g.doubleclick.net/pagead/managed/dict/m202609030101/
63 KB
23 KB
254ms
113ms
Other
text/plain
142.250.154.154
Google LLC
General
Full URL
https://securepubads.g.doubleclick.net/pagead/managed/dict/m202609030101/gpt
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.250.154.154 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bt-in-f154.1e100.net
Software
cafe /
Resource Hash
34e1b5bd04be260f1aff9b3ed448e23488d8e25ff9fdacf020d39b1a86f97c57
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
etag
14501083907114745930
age
21188
x-content-type-options
nosniff
expires
Sun, 13 Sep 2026 13:22:21 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
date
Sun, 06 Sep 2026 13:22:21 GMT
content-type
text/plain; charset=UTF-8
vary
Accept-Encoding
cache-control
public, immutable, max-age=604800, stale-while-revalidate=7200
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
content-length
23722
x-xss-protection
0
server
cafe
use-as-dictionary
match="/gampad/ads?*ptt=17*", id="m202609030101"
GET
H2
200
braze.min.js Show response
js.appboycdn.com/web-sdk/5.6/
217 KB
63 KB
396ms
145ms
Script
application/javascript
104.16.120.9
Cloudflare
General
Full URL
https://js.appboycdn.com/web-sdk/5.6/braze.min.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.16.120.9 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
428ed6d8ac20e15ad2db3d2737d43fc1a00d18bf80847ca51893129bdaf7a935

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-amz-id-2
yUYNKAc/jb2xaBfGfUdFvHwiFoORhtIHshN6+xq4O60x88A4gNL3LMeJnd757Vnn/XBZ23y1gdfkYTzMfJoCZoN/FhIeGFVw
cache-control
public, max-age=14400
content-encoding
gzip
cf-cache-status
HIT
etag
W/"b5a6321ddee88f9ae269f8899487dd3f"
age
6049
x-amz-request-id
WVADTAW431T692AS
expires
Sun, 06 Sep 2026 23:15:30 GMT
cf-ray
a36fcd810bc3d244-FRA
date
Sun, 06 Sep 2026 19:15:30 GMT
content-type
application/javascript; charset=utf-8
last-modified
Thu, 14 Nov 2024 22:49:38 GMT
vary
accept-encoding
server
cloudflare
x-amz-server-side-encryption
AES256
GET
H2
200
vision-media.js Show response
secure.espn.com/js/dcf/tags/vision/latest/
46 KB
18 KB
419ms
115ms
Script
application/x-javascript
184.24.77.190
AKAMAI-ASN1 Akama...
General
Full URL
https://secure.espn.com/js/dcf/tags/vision/latest/vision-media.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
184.24.77.190 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a184-24-77-190.deploy.static.akamaitechnologies.com
Software
AmazonS3 /
Resource Hash
37697dc94d2293590cb41f186d533d1bc820c5f1406537ba500bfde055b87de0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=269
content-encoding
gzip
etag
W/"f06b97aeba6c346cb7bf6b91cdc61225"
access-control-allow-origin
*
content-length
18467
x-amz-cf-id
8H5dWlgf4Og65t-zxg50a5seRdjU40b3QHKjqnpZfeSEy35GNOqKxg==
date
Sun, 06 Sep 2026 19:15:30 GMT
content-type
application/x-javascript
last-modified
Tue, 01 Sep 2026 20:08:14 GMT
server
AmazonS3
x-amz-cf-pop
FRA56-P14
vary
Accept-Encoding
GET
H2
200
beacon.js Show response
sb.scorecardresearch.com/internal-cs/default/
Redirect Chain
  • https://sb.scorecardresearch.com/cs/3000032/beacon.js
  • https://sb.scorecardresearch.com/internal-cs/default/beacon.js
21 KB
7 KB
125ms
124ms
Script
text/javascript
18.244.18.27
Amazon.com
General
Full URL
https://sb.scorecardresearch.com/internal-cs/default/beacon.js
Protocol
H2
Server
18.244.18.27 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-18-244-18-27.fra56.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
7b21bbb8ef971401ae80a3877b20405f18623e70111a65f0503458ea623255ce

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
Referer
https://abc7.com/

Response headers

vary
Accept-Encoding
cache-control
max-age=86400
content-encoding
gzip
etag
W/"3f6dea365716e8ba82711013483c4d83"
age
60232
via
1.1 d025091c574ce1bcf1fefea59ac34f2c.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
B6xw0mxoorzknKFihMFv64B-D4ouupfYE4zeLSQ2pdr8p5g6oHl8Aw==
date
Sun, 06 Sep 2026 02:32:13 GMT
content-type
text/javascript
last-modified
Mon, 08 Sep 2025 12:31:10 GMT
server
AmazonS3
x-amz-cf-pop
FRA56-P11
x-amz-server-side-encryption
AES256

Redirect headers

location
/internal-cs/default/beacon.js
accept-ch
UA, Platform, Arch, Model, Mobile
via
1.1 d025091c574ce1bcf1fefea59ac34f2c.cloudfront.net (CloudFront)
x-cache
Miss from cloudfront
content-length
0
x-amz-cf-id
LrBgxxEraia3mC0MJV5TS5IvtwMD_XmQ2H2ycgSGcL9SSV_ENoy53w==
date
Sun, 06 Sep 2026 19:15:30 GMT
x-amz-cf-pop
FRA56-P11
GET
H2
200
id Show response
disney.demdex.net/
185 B
650 B
420ms
127ms
XHR
application/json
52.51.56.224
Amazon.com
General
Full URL
https://disney.demdex.net/id?d_visid_ver=5.5.0&d_fieldgroup=MC&d_rtbd=json&d_ver=2&d_verify=1&d_orgid=19916ABB53224B2C0A490D45%40AdobeOrg&d_nsid=0&d_coppa=true&ts=1788722129866
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
52.51.56.224 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-52-51-56-224.eu-west-1.compute.amazonaws.com
Software
/
Resource Hash
f7ebd6dda1fdda1f6e5f3896266c0a1b247d362ce2619243cc65e8aa3d86ee3c
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
Content-Type
application/x-www-form-urlencoded
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
no-cache,no-store,must-revalidate,max-age=0,proxy-revalidate,no-transform,private
dcs
dcs-prod-irl1-1-v092-05e659c5f.edge-irl1.demdex.com 1 ms
content-encoding
zstd
pragma
no-cache
access-control-allow-credentials
true
x-tid
eti2Yf1sRe4=
expires
Thu, 01 Jan 1970 00:00:00 UTC
access-control-allow-origin
https://abc7.com
content-length
174
p3p
policyref="/w3c/p3p.xml", CP="NOI NID CURa ADMa DEVa PSAa PSDa OUR SAMa BUS PUR COM NAV INT"
date
Sun, 06 Sep 2026 19:15:30 GMT
content-type
application/json;charset=utf-8
vary
Origin
GET
H2
200
log Show response
log.go.com/
1 B
341 B
675ms
189ms
Fetch
application/octet-stream
15.197.135.246
Amazon.com
General
Full URL
https://log.go.com/log?appid=IDENTITY-SDK-V5&sdk_version=web+5.1.30-qa.0&conversation_id=83449b72-2240-45de-a1d6-9fe425c92d41&language=en-US&sdk_install_id=2627c924-96e2-4c09-a5ce-389cc2d6003e&swid=76d9eb61-6562-4b6d-a09d-8ea2b1296ac4&event_start_time=1788722129689&transaction_id=f6c37951-5052-4cb4-8b0b-6c6e4505699f&info=async%28false%29%2Cresponsestatus%28200%29&action_name=service%3Arefresh%3Asiteconfig&process_time=254&client_id=DATG-OTV.KABC.WEB-PROD&timestamp=1788722129943
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
15.197.135.246 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
a7b7d02f3736e735c.awsglobalaccelerator.com
Software
/
Resource Hash
36a9e7f1c95b82ffb99743e0c5c4ce95d83c9a430aac59f84ef3cbfab6145068

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
900
cache-control
no-cache
pragma
no-cache
access-control-allow-credentials
true
access-control-allow-methods
GET, POST, OPTIONS
allow
GET, OPTIONS
expires
0
access-control-allow-origin
https://abc7.com
date
Sun, 06 Sep 2026 19:15:30 GMT
content-type
application/octet-stream
vary
Origin
GET
H2
200
log Show response
log.go.com/
1 B
343 B
674ms
190ms
Fetch
application/octet-stream
15.197.135.246
Amazon.com
General
Full URL
https://log.go.com/log?appid=IDENTITY-SDK-V5&sdk_version=web+5.1.30-qa.0&conversation_id=6562fe9f-6e9d-4af3-9c89-77365cc49df5&language=en-US&sdk_install_id=2627c924-96e2-4c09-a5ce-389cc2d6003e&detected_country=US&swid=76d9eb61-6562-4b6d-a09d-8ea2b1296ac4&event_start_time=1788722129944&storage_mode=localstorage_only&multi_subdomain_enabled=false&action_name=log%3Astorage%3Ainitialized&process_time=0&client_id=DATG-OTV.KABC.WEB-PROD&timestamp=1788722129944
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
15.197.135.246 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
a7b7d02f3736e735c.awsglobalaccelerator.com
Software
/
Resource Hash
36a9e7f1c95b82ffb99743e0c5c4ce95d83c9a430aac59f84ef3cbfab6145068

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
900
cache-control
no-cache
pragma
no-cache
access-control-allow-credentials
true
access-control-allow-methods
GET, POST, OPTIONS
allow
GET, OPTIONS
expires
0
access-control-allow-origin
https://abc7.com
date
Sun, 06 Sep 2026 19:15:30 GMT
content-type
application/octet-stream
vary
Origin
GET
H2
200
web Show response
login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/ Frame 4730
49 KB
15 KB
339ms
128ms
Document
text/html
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/ Next.js
Resource Hash
f088a58862e063825d7d9073eef18acd4a9d90553d1549d0a0bd5d5bbd0c6425

Request headers

Referer
https://abc7.com/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

age
632
cache-control
public, s-maxage=900, max-age=0, must-revalidate, stale-while-revalidate=60, stale-if-error=900
content-encoding
gzip
content-type
text/html; charset=utf-8
date
Sun, 06 Sep 2026 19:04:58 GMT
vary
RSC,Accept-Encoding
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
x-amz-cf-id
VUYF6T49HodZwfL49j5T2sbuXd8eLwp5To9crmd7JXIaw5SCZ2p4og==
x-amz-cf-pop
FRA56-P10
x-bamtech-region
eu-central-1
x-cache
Hit from cloudfront
x-powered-by
Next.js
x-request-id
e61ca0f27b37e015899a64f7b5f7de3e
GET
H2
200
Symbol_Defs--v49.svg Show response
secure.espncdn.com/i/espnicons/
234 KB
73 KB
382ms
115ms
XHR
image/svg+xml
184.24.77.190
AKAMAI-ASN1 Akama...
General
Full URL
https://secure.espncdn.com/i/espnicons/Symbol_Defs--v49.svg
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
184.24.77.190 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a184-24-77-190.deploy.static.akamaitechnologies.com
Software
AmazonS3 /
Resource Hash
64f9c4b79f2657eefe8c334cc79786ab94c50f216999cb5f32b69b7cc50018ef

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
Accept
application/json, text/plain, */*
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=84
content-encoding
gzip
etag
W/"6725a2d48138092a0e2e2cd78da34a1b"
accept-ranges
bytes
access-control-allow-origin
*
content-length
74857
date
Sun, 06 Sep 2026 19:15:30 GMT
last-modified
Tue, 05 Aug 2025 21:03:21 GMT
vary
Accept-Encoding
server
AmazonS3
content-type
image/svg+xml
POST
H2
204
debug
il-trc-events.taboola.com/abcotvweb-abc7la/log/2/
0
124 B
393ms
112ms
Ping
text/plain
185.106.33.48
TABOOLA-AS Tabool...
General
Full URL
https://il-trc-events.taboola.com/abcotvweb-abc7la/log/2/debug?type=warn&msg=protected%20media%3A%20enableFraudDetection&lt=default&tvi48=32980&tvi50=32540&tim=22%3A15%3A30.196&id=18884&cv=20260906-3-RELEASE&llvl=2
Requested by
Host: cdn.taboola.com
URL: https://cdn.taboola.com/libtrc/abcotvweb-network/loader.js
Protocol
H2
Security
TLS 1.2, ECDHE_ECDSA, AES_128_GCM
Server
185.106.33.48 , Israel, ASN200478 (TABOOLA-AS Taboola.com ltd, IL),
Reverse DNS
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
Content-Type
application/x-www-form-urlencoded
sec-ch-ua-mobile
?0

Response headers

access-control-allow-origin
https://abc7.com
x-fastly-to-nlb-rtt
55525
date
Sun, 06 Sep 2026 19:15:30 GMT
server
nginx
access-control-allow-credentials
true
GET
H2
200
fraud-detect.js Show response
cdn.taboola.com/scripts/
121 B
420 B
344ms
118ms
Script
application/javascript
151.101.193.44
Fastly
General
Full URL
https://cdn.taboola.com/scripts/fraud-detect.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
AmazonS3 /
Resource Hash
392c32f20b9f867852a946a6ed1c5e21476df9619083548b6585d80a3b5f9bd4

Request headers

Origin
https://abc7.com
sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-fastly-object-storage
false
content-encoding
gzip
etag
"f7a185d92ac2162dc0bc36c5d7ef7dfe"
x-amz-version-id
vOXBAr_FxKHpU348.XTQhP6DWnVyKple
age
1482
x-cache
HIT
date
Sun, 06 Sep 2026 19:15:30 GMT
last-modified
Thu, 15 Dec 2022 16:50:08 GMT
x-served-by
cache-fra-eddf8230202-FRA
x-cache-hits
1248
content-type
application/javascript
x-amz-id-2
G+2glYtlqlrBn6smqsilLvqfYhThSGhF1r3JVsCmx1ye1E1VOUoRlKyc/chTurWY5IJ2S+2U95RDXOFSNUas/js/J5EsG/Ky
vary
Accept-Encoding
x-amz-replication-status
COMPLETED
cache-control
private,max-age=14400
x-timer
S1788722130.483762,VS0,VE0
via
1.1 varnish
x-amz-request-id
XATWB6AP49PTXPPC
accept-ranges
bytes
access-control-allow-origin
*
abp
36
content-length
125
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H2
200
firstid.es5.js Show response
cdn.taboola.com/scripts/
1 KB
1 KB
343ms
117ms
Script
application/javascript
151.101.193.44
Fastly
General
Full URL
https://cdn.taboola.com/scripts/firstid.es5.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
AmazonS3 /
Resource Hash
407b44755fe9cc0fda37bfc7028a39963dadf8e97c75c1bcde895508b9ae3a25

Request headers

Origin
https://abc7.com
sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-fastly-object-storage
false
content-encoding
gzip
etag
"991788fef5939f76123d2f43f8cf1696"
x-amz-version-id
Pk_nyAKJa6nUOWdX0QRXRn4VushvsQY4
age
16912
x-cache
HIT, HIT
date
Sun, 06 Sep 2026 19:15:30 GMT
last-modified
Sun, 11 Jan 2026 13:27:32 GMT
x-served-by
cache-iad-kjyo7100143-IAD, cache-fra-eddf8230202-FRA
x-cache-hits
231856, 12132
content-type
application/javascript
x-amz-id-2
LyXd3s+Q356fmeUfTkGMG3j+kbWehVbIymlufDevYzC/RGyPPu2NOXIzovkxt1m4ejZimz+O5WE=
vary
Accept-Encoding
x-amz-replication-status
COMPLETED
cache-control
private,max-age=14400
x-timer
S1788722130.483380,VS0,VE1
via
1.1 varnish, 1.1 varnish
x-amz-request-id
4YYXCYWKRSPD1VJ3
accept-ranges
bytes
access-control-allow-origin
*
abp
13
content-length
591
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H2
200
cds-pips.js Show response
cdn.taboola.com/scripts/
4 KB
2 KB
344ms
118ms
Script
application/javascript
151.101.193.44
Fastly
General
Full URL
https://cdn.taboola.com/scripts/cds-pips.js?dc=il&d=d
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
AmazonS3 /
Resource Hash
df0cf0f3184aebac9d5be7697f6a0cc4156785312b5272c01356b62a86924ffa

Request headers

Origin
https://abc7.com
sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-fastly-object-storage
false
content-encoding
gzip
etag
"3971444f58a5e6520f9de3a53853837d"
x-amz-version-id
2JM2.gkwaRk7BeovQdC9P7R.n.yPIBeR
age
1212
x-cache
HIT
date
Sun, 06 Sep 2026 19:15:30 GMT
last-modified
Wed, 15 Oct 2025 07:00:48 GMT
x-served-by
cache-fra-eddf8230202-FRA
x-cache-hits
2476
content-type
application/javascript
x-amz-id-2
BGlPi/mPViYfAaDnDjnMllJ/mDrwIUUEtqq4b5nW49RTPc+kSvFqx02TTvUpvIzby2KT+D+aMXUOX3edm8/BGQW+dj13HNu6
vary
Accept-Encoding
x-amz-replication-status
COMPLETED
cache-control
private, max-age=3600
x-timer
S1788722130.483334,VS0,VE0
via
1.1 varnish
x-amz-request-id
6QZ8JGHZYYHV8J38
accept-ranges
bytes
access-control-allow-origin
*
abp
81
content-length
1533
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H2
200
bbdacda881389372b02331e50c103ed4.jpg
images.taboola.com/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_489%2Cw_880%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.taboola.com/libtrc/static/thumbnails/
36 KB
37 KB
138ms
136ms
Image
image/webp
151.101.193.44
Fastly
General
Full URL
https://images.taboola.com/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_489%2Cw_880%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.taboola.com/libtrc/static/thumbnails/bbdacda881389372b02331e50c103ed4.jpg
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
nginx /
Resource Hash
a5ad9bb71ebbeaa1816494b7c15968efddca1093f5cfa1c8eb1c3cf4e8d58013

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

etag
"x/9mJlKnE8M8btVB45EyzC3IvzTuSpcCCnefjB88n+Q"
x-amz-version-id
gLiwgAmQp7fRHaPMUA7vnQkJIVfUEm_L
age
2012916
x-cache
HIT, MISS, HIT, MISS, HIT, HIT
content-type
image/webp
x-cache-hits
1, 0, 2, 0, 1, 0
x-amz-replication-status
PENDING
cache-control
public, max-age=31536000
x-envoy-upstream-service-time
363
x-timer
S1788722130.315266,VS0,VE4
x-tbl-io-backend
fastly
x-ratelimit-reset
1
x-amz-request-id
MAWJWYAKTXCZ6MKZ
accept-ranges
bytes
abp
79
content-length
37042
server
nginx
x-amz-server-side-encryption
AES256
fastly-io-info
ifsz=31216 idim=800x450 ifmt=jpeg ofsz=37620 odim=880x489 ofmt=jpeg
x-fastly-object-storage
false
x-debug
/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_489%2Cw_880%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.taboola.com/libtrc/static/thumbnails/bbdacda881389372b02331e50c103ed4.jpg
date
Sun, 06 Sep 2026 19:15:30 GMT
x-served-by
cache-iad-kjyo7100084-IAD, cache-iad-kjyo7100084-IAD, cache-iad-khef600038-IAD, cache-hhr-khhr2060023-HHR, cache-iad-kjyo7100079-IAD, cache-lon4258-LON
vary
ImageFormat
x-amz-id-2
85I5+CPPrnX6js11kLBydIwQCRcA4CTQLNN/TxckSQ6YtRZ9VHXMIoBul7F0wUzntu/DbzolWG+TSVI0gavGwbk0dEIp7Zdf
x-amz-meta-x-tbl-source
taboola-backstage
x-vcl-version
53
x-vcl-time-ms
4
via
1.1 varnish, 1.1 varnish
x-ratelimit-remaining
100
access-control-allow-origin
*
fastly-io-served-by
vpop-kiad7010228
x-ratelimit-limit
101
fastly-io-transform-stats
ifsz=31216 ofsz=37620 ofmt=jpeg
GET
H2
200
cd04d3fae5e557dc2deca93fab032992.jpg
images.taboola.com/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_245%2Cw_440%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.taboola.com/libtrc/static/thumbnails/
13 KB
14 KB
123ms
122ms
Image
image/webp
151.101.193.44
Fastly
General
Full URL
https://images.taboola.com/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_245%2Cw_440%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.taboola.com/libtrc/static/thumbnails/cd04d3fae5e557dc2deca93fab032992.jpg
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
nginx /
Resource Hash
7d12b981a1720c1846ff999befe5ebae5615edba2e15dcd6f33ba5006a1fd3f5

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

etag
"46Kz0gmN35grgAVhi5CxLVLrwpaaUnTrC/t/pGCgpos"
x-amz-version-id
ewhFEWHlUCjPdKOQWbfEftyPt7ShUQK8
age
786610
x-cache
HIT, MISS, HIT, MISS, HIT, HIT
content-type
image/webp
x-cache-hits
1, 0, 6, 0, 3, 1
x-amz-replication-status
FAILED
cache-control
public, max-age=31536000
x-envoy-upstream-service-time
126
x-timer
S1788722130.315241,VS0,VE1
x-tbl-io-backend
fastly
x-ratelimit-reset
1
x-amz-request-id
QDH0JNBSZF5KXKXE
accept-ranges
bytes
abp
65
content-length
12992
server
nginx
x-amz-server-side-encryption
AES256
fastly-io-info
ifsz=143305 idim=1200x674 ifmt=jpeg ofsz=16030 odim=600x333 ofmt=jpeg
x-fastly-object-storage
false
x-debug
/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_245%2Cw_440%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.taboola.com/libtrc/static/thumbnails/cd04d3fae5e557dc2deca93fab032992.jpg
date
Sun, 06 Sep 2026 19:15:30 GMT
x-served-by
cache-iad-kjyo7100054-IAD, cache-iad-kjyo7100054-IAD, cache-iad-kjyo7100049-IAD, cache-lax-kwhp1940035-LAX, cache-iad-kcgs7200168-IAD, cache-lon4258-LON
vary
ImageFormat
x-amz-id-2
TAKjVd4FGs1uLqKVkLk/yPLeUPkHFEN/RV1QpluSsJW5A2CFUJgrj6T9+MN1bgBhSgo01WJJVN3kueYhdH3bFh5RtpInJGXW
x-amz-meta-x-tbl-source
taboola-backstage
x-vcl-version
53
x-vcl-time-ms
1
via
1.1 varnish, 1.1 varnish
x-ratelimit-remaining
100
access-control-allow-origin
*
req-referer
https://www.ynet.co.il/
fastly-io-served-by
img31-us-east4
x-ratelimit-limit
101
fastly-io-transform-stats
ifsz=143305 ofsz=16030 ofmt=jpeg
GET
H2
200
0f6abab409d21502b6c06047d214623a.png
images.taboola.com/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_245%2Cw_440%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.taboola.com/libtrc/static/thumbnails/
19 KB
20 KB
123ms
122ms
Image
image/webp
151.101.193.44
Fastly
General
Full URL
https://images.taboola.com/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_245%2Cw_440%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.taboola.com/libtrc/static/thumbnails/0f6abab409d21502b6c06047d214623a.png
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
nginx /
Resource Hash
01ea0b315c71d3175f0361f8af9fcacf8df0324023115452dc74409beed3064b

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

etag
"XYENr+mmEmsyFkk/7CxPQrlS2Cbu2tBQu91LoAbyMQs"
x-amz-version-id
pXNR0GfGGa_Pv7SPPCtMiFlwUSzYMQGP
age
431607
x-cache
HIT, MISS, HIT, HIT, HIT
content-type
image/webp
x-cache-hits
1, 0, 0, 14, 0
x-amz-replication-status
PENDING
cache-control
public, max-age=31536000
x-envoy-upstream-service-time
136
x-timer
S1788722130.315223,VS0,VE1
x-tbl-io-backend
fastly
x-ratelimit-reset
1
x-amz-request-id
5QW7G54EK9ZY7C2A
accept-ranges
bytes
abp
16
content-length
19814
server
nginx
x-amz-server-side-encryption
AES256
fastly-io-info
ifsz=1067021 idim=1200x800 ifmt=png ofsz=24231 odim=600x333 ofmt=jpeg
x-fastly-object-storage
false
x-debug
/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_245%2Cw_440%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.taboola.com/libtrc/static/thumbnails/0f6abab409d21502b6c06047d214623a.png
date
Sun, 06 Sep 2026 19:15:30 GMT
x-served-by
cache-iad-kiad7000128-IAD, cache-iad-kiad7000128-IAD, cache-iad-kiad7000083-IAD, cache-iad-kcgs7200071-IAD, cache-lon4258-LON
vary
ImageFormat
x-amz-id-2
ejyLJu2rWcf2AKqraIaUTxpwnc/PYeEbAD6XzEhnk8j3T8RYrP648fBAftHVw5Tk540c6So607gLCiWspRQhgLbpuYAWj4yZ
x-amz-meta-x-tbl-source
taboola-backstage
x-vcl-version
53
x-vcl-time-ms
1
via
1.1 varnish, 1.1 varnish
x-ratelimit-remaining
100
access-control-allow-origin
*
req-referer
https://www.ynet.co.il/
fastly-io-served-by
img24-us-east4
x-ratelimit-limit
101
fastly-io-transform-stats
ifsz=1067021 ofsz=24231 ofmt=jpeg
GET
H2
200
3a57344424e731e5c579bc83df92af5c.jpg
images.taboola.com/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_489%2Cw_880%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.taboola.com/libtrc/static/thumbnails/
66 KB
67 KB
123ms
122ms
Image
image/webp
151.101.193.44
Fastly
General
Full URL
https://images.taboola.com/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_489%2Cw_880%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.taboola.com/libtrc/static/thumbnails/3a57344424e731e5c579bc83df92af5c.jpg
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
nginx /
Resource Hash
9658f67951a525cdce614ff70386f917e33fd695ccac49d803ea53a6736eb443

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

etag
"fL2ZJixIB4qtlB30HOC7mtjmYVSnnl1Z8YTCQHXw228"
x-amz-version-id
ePi6ZtMMfttt8N9LycKrfbh6BuM9RFg5
age
535349
x-cache
HIT, MISS, HIT, HIT, HIT, HIT
content-type
image/webp
x-cache-hits
1, 0, 3, 1, 6, 0
x-amz-replication-status
PENDING
cache-control
public, max-age=31536000
x-envoy-upstream-service-time
270
x-timer
S1788722130.315196,VS0,VE1
x-tbl-io-backend
fastly
x-ratelimit-reset
1
x-amz-request-id
5ATHGS1MXHHC3FBT
accept-ranges
bytes
abp
38
content-length
68054
server
nginx
x-amz-server-side-encryption
AES256
fastly-io-info
ifsz=901467 idim=1200x1200 ifmt=jpeg ofsz=100171 odim=1200x667 ofmt=jpeg
x-fastly-object-storage
false
x-debug
/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_489%2Cw_880%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.taboola.com/libtrc/static/thumbnails/3a57344424e731e5c579bc83df92af5c.jpg
date
Sun, 06 Sep 2026 19:15:30 GMT
x-served-by
cache-iad-kiad7000079-IAD, cache-iad-kiad7000079-IAD, cache-iad-kiad7000122-IAD, cache-nyc-kteb1890022-NYC, cache-iad-kiad7000170-IAD, cache-lon4258-LON
vary
ImageFormat
x-amz-id-2
cc3S6fQ78KY4przVZR4rWJXdjvAapEwGewJ96DOfcir2rzjP7WGMyz/oMRvi6wQFg3IuYFm6jA0=
x-amz-meta-x-tbl-source
taboola-backstage
x-vcl-version
53
x-vcl-time-ms
1
via
1.1 varnish, 1.1 varnish
x-ratelimit-remaining
100
access-control-allow-origin
*
fastly-io-served-by
img10-us-east4
x-ratelimit-limit
101
fastly-io-transform-stats
ifsz=901467 ofsz=100171 ofmt=jpeg
GET
H2
200
6d04d847-8012-4963-ba85-c43d544dcb16__bdMgEPtc.jpg
images.taboola.com/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_245%2Cw_440%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/http%3A//cdn.taboola.com/libtrc/static/thumbnails/STABLE_DIFFUSION_OUTCROP/ESD/
23 KB
23 KB
125ms
124ms
Image
image/webp
151.101.193.44
Fastly
General
Full URL
https://images.taboola.com/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_245%2Cw_440%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/http%3A//cdn.taboola.com/libtrc/static/thumbnails/STABLE_DIFFUSION_OUTCROP/ESD/6d04d847-8012-4963-ba85-c43d544dcb16__bdMgEPtc.jpg
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
nginx /
Resource Hash
6f254afec2706c99d47a5c0bb30367341669b8dfc98fc2625bf5a185bfe10826

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

etag
"3z4JTb9chqLKLoVSZP0P163snqrklF7COBnxJ+Pf6sY"
x-amz-version-id
wgKGODspxGxXl2VMBpSlLp1kj3ycZx0P
age
1697836
x-cache
HIT, MISS, HIT, HIT, HIT, HIT
content-type
image/webp
x-cache-hits
0, 0, 8, 0, 2, 0
x-amz-replication-status
COMPLETED
cache-control
public, max-age=31536000
x-envoy-upstream-service-time
47
x-timer
S1788722130.315143,VS0,VE2
x-tbl-io-backend
fastly
x-ratelimit-reset
1
x-amz-request-id
18RZG23FD6RGSKH7
accept-ranges
bytes
abp
2
content-length
23044
server
nginx
x-amz-server-side-encryption
AES256
fastly-io-info
ifsz=799183 idim=2160x1920 ifmt=jpeg ofsz=78392 odim=1080x600 ofmt=jpeg
x-fastly-object-storage
false
x-debug
/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_245%2Cw_440%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/http%3A//cdn.taboola.com/libtrc/static/thumbnails/STABLE_DIFFUSION_OUTCROP/ESD/6d04d847-8012-4963-ba85-c43d544dcb16__bdMgEPtc.jpg
date
Sun, 06 Sep 2026 19:15:30 GMT
x-served-by
cache-iad-kiad7000023-IAD, cache-iad-kiad7000023-IAD, cache-iad-kjyo7100064-IAD, cache-nrt-rjtf7700027-NRT, cache-iad-kcgs7200058-IAD, cache-lon4258-LON
vary
ImageFormat
x-amz-id-2
u3kSKPjByWL3Ba56x/hTeAtTPxTMtli1ms6K3l+vFs/Cs+Lzkh5K3Onl8v5/y4gwhTZtVHsZ6Z/APeCpfVDkbWKwG8DUxqEY
x-vcl-version
53
x-vcl-time-ms
2
via
1.1 varnish, 1.1 varnish
x-ratelimit-remaining
100
access-control-allow-origin
*
req-referer
https://13tv.co.il/
fastly-io-served-by
img07-us-east4
x-ratelimit-limit
101
fastly-io-transform-stats
ifsz=799183 ofsz=78392 ofmt=jpeg
GET
H2
200
98e2f32f9947169b109ec2cd0e44d36c.png
images.taboola.com/taboola/image/fetch/c_crop%2Cf_jpg%2Cq_auto%2Ce_sharpen%2Car_1.7778%2Cw_1080%2Cx_0%2Cy_21/c_fill%2Cw_440%2Ch_245/http%3A//cdn.taboola.com/libtrc/static/thumbnails/
16 KB
16 KB
118ms
118ms
Image
image/webp
151.101.193.44
Fastly
General
Full URL
https://images.taboola.com/taboola/image/fetch/c_crop%2Cf_jpg%2Cq_auto%2Ce_sharpen%2Car_1.7778%2Cw_1080%2Cx_0%2Cy_21/c_fill%2Cw_440%2Ch_245/http%3A//cdn.taboola.com/libtrc/static/thumbnails/98e2f32f9947169b109ec2cd0e44d36c.png
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
nginx /
Resource Hash
a5e4d8a41d73f6aaa7e18a28c0b7e5343f5ffa594e184af43c1900f5b851cf5a

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-debug
/taboola/image/fetch/c_crop%2Cf_jpg%2Cq_auto%2Ce_sharpen%2Car_1.7778%2Cw_1080%2Cx_0%2Cy_21/c_fill%2Cw_440%2Ch_245/http%3A//cdn.taboola.com/libtrc/static/thumbnails/98e2f32f9947169b109ec2cd0e44d36c.png
age
777395
x-cache
MISS, HIT
date
Sun, 06 Sep 2026 19:15:30 GMT
content-type
image/webp
x-served-by
cache-iad-kiad7000136-IAD, cache-lon4258-LON
x-cache-hits
0, 0
vary
ImageFormat
cache-control
public, max-age=31536000
x-envoy-upstream-service-time
653
x-timer
S1788722130.313193,VS0,VE1
x-vcl-time-ms
1
x-ratelimit-reset
1
via
1.1 varnish, 1.1 varnish
x-ratelimit-remaining
100
accept-ranges
bytes
req-referer
https://timeout.co.il/
content-length
16032
x-ratelimit-limit
101
server
nginx
GET
H2
200
1db92686391886d72bd776ced259817b.jpg
images.taboola.com/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_489%2Cw_880%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.taboola.com/libtrc/static/thumbnails/
143 KB
144 KB
120ms
117ms
Image
image/webp
151.101.193.44
Fastly
General
Full URL
https://images.taboola.com/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_489%2Cw_880%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.taboola.com/libtrc/static/thumbnails/1db92686391886d72bd776ced259817b.jpg
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
nginx /
Resource Hash
e5786471e800d6b43f40b9d6cfe353cc81212ae3b6e415fd27b32a043f47c27a

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

etag
"ALi8Jspo9boKaiPr8Evr3FRUWIpeBgDKFXMPaAegBWM"
x-amz-version-id
qIQfSiA036_qn6KMNin9u.eDBqI2N8QY
age
1075379
x-cache
HIT, MISS, HIT, HIT, HIT, HIT
content-type
image/webp
x-cache-hits
1, 0, 6, 0, 2, 0
x-amz-replication-status
PENDING
cache-control
public, max-age=31536000
x-envoy-upstream-service-time
550
x-timer
S1788722130.436168,VS0,VE2
x-tbl-io-backend
fastly
x-ratelimit-reset
1
x-amz-request-id
HAHEPRRG34W516ZF
accept-ranges
bytes
abp
28
content-length
146220
server
nginx
x-amz-server-side-encryption
AES256
fastly-io-info
ifsz=231133 idim=1024x572 ifmt=jpeg ofsz=130258 odim=1024x569 ofmt=jpeg
x-fastly-object-storage
false
x-debug
/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_489%2Cw_880%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.taboola.com/libtrc/static/thumbnails/1db92686391886d72bd776ced259817b.jpg
date
Sun, 06 Sep 2026 19:15:30 GMT
x-served-by
cache-iad-kiad7000049-IAD, cache-iad-kiad7000049-IAD, cache-iad-kiad7000049-IAD, cache-ams-eham8680059-AMS, cache-iad-kiad7000153-IAD, cache-lon4258-LON
vary
ImageFormat
x-amz-id-2
C67cHXKQNIQMcRaMrUAYpNtsBjLbN9FRWsauZPZvuz3a+QG/el5EDZ/4CTcNUCZmjmSGXS5C/Ok=
x-amz-meta-x-tbl-source
taboola-backstage
x-vcl-version
53
x-vcl-time-ms
2
via
1.1 varnish, 1.1 varnish
x-ratelimit-remaining
100
access-control-allow-origin
*
fastly-io-served-by
img27-us-east4
x-ratelimit-limit
101
fastly-io-transform-stats
ifsz=231133 ofsz=130258 ofmt=jpeg
GET
H2
200
ea21b94476ee43501cf3d22579680fba.png
images.taboola.com/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_245%2Cw_440%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.taboola.com/libtrc/static/thumbnails/
13 KB
14 KB
136ms
135ms
Image
image/webp
151.101.193.44
Fastly
General
Full URL
https://images.taboola.com/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_245%2Cw_440%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.taboola.com/libtrc/static/thumbnails/ea21b94476ee43501cf3d22579680fba.png
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
nginx /
Resource Hash
42cfe8d25d608a7f13f218ca007f8c74665651e0b113397ee4ed8b48fcfddeed

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

etag
"QGm5Rt5wQZo4HTH/ZiKQT+oIv0Auli+M/bqoo78fpxU"
x-amz-version-id
Nr9rzfgGQF0RKdIs_yHDMyvPIrFsQyZT
age
216169
x-cache
HIT, MISS, MISS, HIT, HIT, HIT
content-type
image/webp
x-cache-hits
1, 0, 0, 1, 4, 0
x-amz-replication-status
FAILED
cache-control
public, max-age=31536000
x-envoy-upstream-service-time
79
x-timer
S1788722130.438169,VS0,VE1
x-tbl-io-backend
fastly
x-ratelimit-reset
1
x-amz-request-id
PQXVZ2ZCQP8Z0XQF
accept-ranges
bytes
abp
2
content-length
13424
server
nginx
x-amz-server-side-encryption
AES256
fastly-io-info
ifsz=461428 idim=750x500 ifmt=png ofsz=27378 odim=750x417 ofmt=jpeg
x-fastly-object-storage
false
x-debug
/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_245%2Cw_440%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.taboola.com/libtrc/static/thumbnails/ea21b94476ee43501cf3d22579680fba.png
date
Sun, 06 Sep 2026 19:15:30 GMT
x-served-by
cache-iad-kjyo7100143-IAD, cache-iad-kjyo7100143-IAD, cache-iad-kiad7000127-IAD, cache-nyc-kteb1890025-NYC, cache-iad-kiad7000177-IAD, cache-lon4258-LON
vary
ImageFormat
x-amz-id-2
HgyQqwAMiAeEa8RPBa1HvEeIEwmT/TKdRpdffxJuwtdFHp/knjjMBI87nB4MzvJ9PagCj2afSs8=
x-amz-meta-x-tbl-source
taboola-backstage
x-vcl-version
51
x-vcl-time-ms
1
via
1.1 varnish, 1.1 varnish
x-ratelimit-remaining
100
access-control-allow-origin
*
req-referer
https://www.9tv.co.il/
fastly-io-served-by
img04-us-east4
x-ratelimit-limit
101
fastly-io-transform-stats
ifsz=461428 ofsz=27378 ofmt=jpeg
GET
H2
200
c20b6a2dbb559d7263780e896845667e.jpg
images.taboola.com/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_245%2Cw_440%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/http%3A//cdn.taboola.com/libtrc/static/thumbnails/
13 KB
14 KB
135ms
134ms
Image
image/webp
151.101.193.44
Fastly
General
Full URL
https://images.taboola.com/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_245%2Cw_440%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/http%3A//cdn.taboola.com/libtrc/static/thumbnails/c20b6a2dbb559d7263780e896845667e.jpg
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
nginx /
Resource Hash
9bbd117418ef6e3040226c2fcd6659d48c5b23ab386ef22c78cfb1422b46c704

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

etag
"/e+JAMnOLp3T5uX2BWBcjhDi1PIuv0RMpqYNHqGj81A"
x-amz-version-id
_SmVsyQMm86IQtvVVmibvmOc2c0grdcE
age
472169
x-cache
HIT, MISS, HIT, HIT, HIT, HIT
content-type
image/webp
x-cache-hits
1, 0, 1, 0, 8, 0
x-amz-replication-status
COMPLETED
cache-control
public, max-age=31536000
x-envoy-upstream-service-time
268
x-timer
S1788722130.440405,VS0,VE1
x-tbl-io-backend
fastly
x-ratelimit-reset
1
x-amz-request-id
FX9K403S77EX2TA4
accept-ranges
bytes
abp
91
content-length
13244
server
nginx
x-amz-server-side-encryption
AES256
fastly-io-info
ifsz=26831 idim=800x420 ifmt=jpeg ofsz=23827 odim=756x420 ofmt=jpeg
x-fastly-object-storage
false
x-debug
/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_245%2Cw_440%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/http%3A//cdn.taboola.com/libtrc/static/thumbnails/c20b6a2dbb559d7263780e896845667e.jpg
date
Sun, 06 Sep 2026 19:15:30 GMT
x-served-by
cache-iad-kcgs7200109-IAD, cache-iad-kcgs7200109-IAD, cache-iad-kiad7000094-IAD, cache-fra-eddf8230232-FRA, cache-iad-khef600069-IAD, cache-lon4258-LON
vary
ImageFormat
x-amz-id-2
yZIj8gOwH+5qzuWvGVruTswupJ/HLzdV39XdIL7nosV+iFhEQZpYYBtj6/7osdiIYaYw2dfYcsixmcCH7jPFUGGNEMDeI0qa
x-vcl-version
53
x-vcl-time-ms
1
via
1.1 varnish, 1.1 varnish
x-ratelimit-remaining
100
access-control-allow-origin
*
req-referer
https://www.thairath.co.th/
fastly-io-served-by
vpop-kiad7010250
x-ratelimit-limit
101
fastly-io-transform-stats
ifsz=26831 ofsz=23827 ofmt=jpeg
POST
H2
200
json Show response
trc.taboola.com/abcotvweb-abc7la/trc/3/
10 KB
5 KB
300ms
300ms
Fetch
application/javascript
151.101.193.44
Fastly
General
Full URL
https://trc.taboola.com/abcotvweb-abc7la/trc/3/json?llvl=2&tim=22%3A15%3A30.251&lti=default&pubit=n&t=1&data=%7B%22cmps%22%3A0%2C%22gpp%22%3A%22DBABLA~BVQqAAAAAAJY.QA%22%2C%22gpp_sid%22%3A%227%22%2C%22id%22%3A%2214590%22%2C%22sd%22%3A%22v2_7a0184b4d04419d9fefd4a3907c84a9a_419acdb7-b09e-4b32-b034-56c31d5fd705-tuct11974151_1788722129_1788722129_CNawjgYQ35dLGNzUlsGHNCABKAEwZjiI6wpAsJAQSLzS2ANQ____________AVgAYABo9NCqw8yK475ycAGAAQCIAQCQAQA%22%2C%22ui%22%3A%22419acdb7-b09e-4b32-b034-56c31d5fd705-tuct11974151%22%2C%22ii%22%3A%22%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%22%2C%22it%22%3A%22text%22%2C%22vi%22%3A1788722129500%2C%22cv%22%3A%2220260906-3-RELEASE%22%2C%22uiv%22%3A%22default%22%2C%22u%22%3A%22https%3A%2F%2Fabc7.com%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F%22%2C%22qs%22%3A%22%22%2C%22bv%22%3A%220%22%2C%22btv%22%3A%220%22%2C%22ul%22%3A%5B%22he-IL%22%5D%2C%22cos%22%3A%224g%22%2C%22bu%22%3A%22https%3A%2F%2Fabc7.com%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F%22%2C%22vpi%22%3A%22%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%22%2C%22bad%22%3A-1%2C%22sw%22%3A1600%2C%22sh%22%3A1200%2C%22bw%22%3A1600%2C%22bh%22%3A1200%2C%22dw%22%3A1600%2C%22dh%22%3A4886%2C%22sde%22%3A%221.000%22%2C%22lt%22%3A%22default%22%2C%22nsid%22%3A%22abcotvweb-network%22%2C%22r%22%3A%5B%7B%22li%22%3A%22rbox-t2m%22%2C%22uip%22%3A%22Below%20Article%20Thumbnails%20%7C%20Lazy%20Injected%201%22%2C%22orig_uip%22%3A%22Below%20Article%20Thumbnails%20%7C%20Injected%201%22%2C%22s%22%3A1%2C%22uim%22%3A%22above-the-feed-premium-card-fp-delta%3Apub%3Dabcotvweb-network%3Aabp%3D0%22%2C%22fl%22%3A%22ap270QAPPlguu9qXunoADIpxiHb7Y8aTX1SyUQ%3D%3D%22%2C%22ori%22%3A%2226cb070c8afc1401529032001e96cd96%22%2C%22cd%22%3A1890.14%2C%22mw%22%3A538.5%7D%5D%2C%22rtui%22%3A%22cLSeel95TTZRTHgxeUpmb2VxV0JISEF0TDVEU0FmUCUyQnhVQlFWOVh3cTVPMTRoNnR6cjQ5dWJ3WVZacmwyTUZtZnB1dzQ%22%2C%22plf%22%3A%7B%22stop_tslt%22%3Atrue%7D%2C%22uad%22%3A%7B%22mobile%22%3Afalse%2C%22model%22%3A%22%22%2C%22platform%22%3A%22Linux%22%2C%22platformVersion%22%3A%22%22%2C%22uaFullVersion%22%3A%22152.0.7977.82%22%7D%2C%22cacheKey%22%3A%22text%3D%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2CBelow%20Article%20Thumbnails%20%7C%20Lazy%20Injected%201%3Dabove-the-feed-premium-card-fp-delta%3Apub%3Dabcotvweb-network%3Aabp%3D0%22%2C%22_cn%22%3A%22tions_2%22%2C%22lbt%22%3A1788686697209%2C%22uifp%22%3A%22419acdb7-b09e-4b32-b034-56c31d5fd705-tuct11974151%22%2C%22wc%22%3Atrue%2C%22bs%22%3A%7B%22at%22%3A1%2C%22zm%22%3A0%2C%22ls%22%3Atrue%2C%22lm%22%3A-1%2C%22lt%22%3A-1%7D%7D
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
nginx /
Resource Hash
80ca4a0041d7e666b69d4e15ad7667536837c7808d32440b82530a6dec26c06e

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
Content-Type
text/plain
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-cache
MISS
p3p
policyref="http://trc.taboola.com/p3p.xml", CP="NOI DSP COR LAW NID CURa ADMa DEVa PSAa PSDa OUR BUS IND UNI COM NAV INT DEM"
x-log-content-encoding
gzip
date
Sun, 06 Sep 2026 19:15:30 GMT
content-type
application/javascript; charset=utf-8
x-served-by
cache-lon4258-LON
x-cache-hits
0
vary
Accept-Encoding
x-fastly-to-nlb-rtt
81725
x-timer
S1788722130.313263,VS0,VE180
x-vcl-time-ms
180
access-control-allow-credentials
true
via
1.1 varnish
cpu
0.6001041666666667
accept-ranges
bytes
access-control-allow-origin
https://abc7.com
x-service-version
v1
server
nginx
GET
H2
200
UnitInstreamDesktop.min.js Show response
vidstat.taboola.com/lite-unit/5.7.7/
134 KB
33 KB
374ms
135ms
Script
application/javascript
151.101.1.44
Fastly
General
Full URL
https://vidstat.taboola.com/lite-unit/5.7.7/UnitInstreamDesktop.min.js
Requested by
Host: cdn.taboola.com
URL: https://cdn.taboola.com/libtrc/abcotvweb-network/loader.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.1.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
AmazonS3 /
Resource Hash
d5e134e1d02302b8baf04227611266671da29a2b9db0fb69732a56504be791da

Request headers

Origin
https://abc7.com
sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
"93f0a193f4c2046f0eae8f931a946e44"
age
1431152
access-control-allow-methods
GET, OPTIONS, HEAD
x-cache
HIT
date
Sun, 06 Sep 2026 19:15:30 GMT
last-modified
Wed, 05 Aug 2026 08:04:31 GMT
x-served-by
cache-fra-eddf8230135-FRA
x-cache-hits
9192
content-type
application/javascript
x-amz-id-2
NWQBglkgIW3oTKo5YJhuVu7SjXudFQ9HlWvZnON/ACIzxMMN7S0sGHadSF4j8o8xKNpH+hTUwVg=
access-control-allow-headers
*
vary
Accept-Encoding
cache-control
public, max-age=2592000
x-timer
S1788722131.584405,VS0,VE0
via
1.1 varnish
x-amz-request-id
KJYW8KKYF5YW8DXA
accept-ranges
bytes
access-control-allow-origin
*
content-length
33258
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H2
200
UnitFeedManagerDesktop.min.js Show response
vidstat.taboola.com/lite-unit/5.7.7/
135 KB
33 KB
319ms
115ms
Script
application/javascript
151.101.1.44
Fastly
General
Full URL
https://vidstat.taboola.com/lite-unit/5.7.7/UnitFeedManagerDesktop.min.js
Requested by
Host: cdn.taboola.com
URL: https://cdn.taboola.com/libtrc/abcotvweb-network/loader.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.1.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
AmazonS3 /
Resource Hash
0b48cb5b028adec11c79f33dd87dae567f94305c25c9cfc49a8df5a174daa7f2

Request headers

Origin
https://abc7.com
sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
"1bb401a0b4185a6672f070e2b2ebd760"
age
1734776
access-control-allow-methods
GET, OPTIONS, HEAD
x-cache
HIT
date
Sun, 06 Sep 2026 19:15:30 GMT
last-modified
Wed, 05 Aug 2026 08:04:30 GMT
x-served-by
cache-fra-eddf8230135-FRA
x-cache-hits
28458
content-type
application/javascript
x-amz-id-2
kirM+3U60eRpAqbf75ECXAk1ske402qcNNjJXyzY8eF9z8YZiQoRGfOs0QCpg7Yk7zPyxy74T/o=
access-control-allow-headers
*
vary
Accept-Encoding
cache-control
public, max-age=2592000
x-timer
S1788722131.584494,VS0,VE0
via
1.1 varnish
x-amz-request-id
DXDN7S340D7HRZNA
accept-ranges
bytes
access-control-allow-origin
*
content-length
33284
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H2
200
19799143_090626-wls-ap-bruce-campbell-img.jpg%3Fw%3D1600
images.taboola.com/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_550%2Cw_880%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.abcotvs.com/dip/images/
44 KB
45 KB
124ms
124ms
Image
image/webp
151.101.193.44
Fastly
General
Full URL
https://images.taboola.com/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_550%2Cw_880%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.abcotvs.com/dip/images/19799143_090626-wls-ap-bruce-campbell-img.jpg%3Fw%3D1600
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
nginx /
Resource Hash
5859ae8a73c6c9fe22e22904e81130d67a4c80e52ddc9c15bd45a7bb5cae4479
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
20a9b2fdc6992dcf0ddff0d3515d5a6b
access-control-expose-headers
Content-Length,ETag,Server-Timing,X-Content-Type-Options
etag
"qXo8Cc+HsNGWLzQnp08MvPtecOx/Px3WlZMwqPkuZHU"
age
7087
x-content-type-options
nosniff
server-timing
cld-fastly;mitm=fa;dur=2;cpu=1;start=2026-09-06T17:17:23.392Z;desc=hit,rtt;dur=0,content-info;desc="width=1500,height=900,bytes=165976,format=\"jpg\",owidth=1600,oheight=900,obytes=696720,oformat=\"jpg\",crt=1788714900,ocrt=1788714899,ef=(1,13,17,23,30)"
x-cache
MISS, HIT, HIT
content-type
image/webp
x-cache-hits
0, 67, 0
cache-control
public, max-age=31536000
x-envoy-upstream-service-time
372
x-timer
S1788722130.452737,VS0,VE2
x-tbl-io-backend
cloudinary-fastly-fallback
x-ratelimit-reset
1
accept-ranges
bytes
content-length
45414
server
nginx
fastly-io-info
ifsz=165976 idim=1500x900 ifmt=jpeg ofsz=160923 odim=1500x900 ofmt=jpeg
x-debug
/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_550%2Cw_880%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.abcotvs.com/dip/images/19799143_090626-wls-ap-bruce-campbell-img.jpg%3Fw%3D1600
date
Sun, 06 Sep 2026 19:15:30 GMT
x-served-by
cache-iad-kiad7000045-IAD, cache-iad-kiad7000126-IAD, cache-lon4258-LON
vary
ImageFormat
x-vcl-version
53
timing-allow-origin
*
x-vcl-time-ms
2
via
1.1 varnish, 1.1 varnish
x-ratelimit-remaining
100
x-tbl-io-error
fastly_io_error_400_Bad Request
access-control-allow-origin
*
req-referer
https://abc7.com/
fastly-io-served-by
img10-us-east4
x-ratelimit-limit
101
fastly-io-transform-stats
ifsz=165976 ofsz=160923 ofmt=jpeg
GET
H2
200
19747785_AP26234106193006.jpg%3Fw%3D1600
images.taboola.com/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_550%2Cw_880%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.abcotvs.com/dip/images/
122 KB
123 KB
123ms
122ms
Image
image/webp
151.101.193.44
Fastly
General
Full URL
https://images.taboola.com/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_550%2Cw_880%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.abcotvs.com/dip/images/19747785_AP26234106193006.jpg%3Fw%3D1600
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
nginx /
Resource Hash
0db8d6c0e1e16c5e60b59a908ba8dc5eb7196f539838d26d10b527fbc8e6cdd3
Security Headers
Name Value
Strict-Transport-Security max-age=604800
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
ebb2b8549d4b05cac697d49b26732047
access-control-expose-headers
Content-Length,ETag,Server-Timing,X-Content-Type-Options
etag
"31iC6OfhASiIwMaxjInA24U6yLRCoKr1BSCM2ZX6NhI"
age
844386
x-content-type-options
nosniff
server-timing
cld-fastly;mitm=fa;dur=839;cpu=1;start=2026-08-28T00:42:22.535Z;desc=miss,rtt;dur=0,content-info;desc="width=1500,height=900,bytes=403955,format=\"jpg\",owidth=1600,oheight=900,obytes=1204653,oformat=\"jpg\",crt=1787877743,ocrt=1787877742,ef=(1,13,17,23,30)",cloudinary;dur=823;start=2026-08-28T00:42:22.544Z,cld-id;desc=ebb2b8549d4b05cac697d49b26732047
x-cache
HIT, HIT, HIT, HIT
content-type
image/webp
x-cache-hits
1, 0, 79, 0
cache-control
public, max-age=31536000
x-envoy-upstream-service-time
3206
x-timer
S1788722130.453775,VS0,VE1
x-tbl-io-backend
fastly
x-ratelimit-reset
1
accept-ranges
bytes
content-length
125370
server
nginx
fastly-io-info
ifsz=403955 idim=1500x900 ifmt=jpeg ofsz=220183 odim=1500x900 ofmt=jpeg
x-debug
/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_550%2Cw_880%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.abcotvs.com/dip/images/19747785_AP26234106193006.jpg%3Fw%3D1600
date
Sun, 06 Sep 2026 19:15:30 GMT
x-served-by
cache-iad-kiad7000167-IAD, cache-fra-eddf8230058-FRA, cache-iad-kcgs7200154-IAD, cache-lon4258-LON
vary
ImageFormat
strict-transport-security
max-age=604800
x-vcl-version
53
timing-allow-origin
*
x-vcl-time-ms
1
via
1.1 varnish, 1.1 varnish
x-ratelimit-remaining
100
access-control-allow-origin
*
req-referer
https://abc13.com/
fastly-io-served-by
vpop-kiad7010246
x-ratelimit-limit
101
fastly-io-transform-stats
ifsz=403955 ofsz=220183 ofmt=jpeg
GET
H2
200
b61de851db2c8b443fe543ebd957d14b.jpg
images.taboola.com/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_550%2Cw_880%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/http%3A//cdn.taboola.com/libtrc/static/thumbnails/
17 KB
18 KB
194ms
194ms
Image
image/webp
151.101.193.44
Fastly
General
Full URL
https://images.taboola.com/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_550%2Cw_880%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/http%3A//cdn.taboola.com/libtrc/static/thumbnails/b61de851db2c8b443fe543ebd957d14b.jpg
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
nginx /
Resource Hash
4b4d9a2d347d355d5cda04521eaf80fdecee375cc359974bcd74e450de1907bd

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

etag
"FmvFlGgQOZFQ+MkUt/WwDJYffuDpS6fIqtco6w8W5KI"
x-amz-version-id
8OLjTkJJUKh7D5._feQXBPZtWq5PcnAl
age
162094
x-cache
HIT, MISS, MISS, HIT, HIT, MISS
content-type
image/webp
x-cache-hits
0, 0, 0, 0, 2, 0
x-amz-replication-status
COMPLETED
cache-control
public, max-age=31536000
x-envoy-upstream-service-time
194
x-timer
S1788722130.457609,VS0,VE77
x-tbl-io-backend
fastly
x-ratelimit-reset
1
x-amz-request-id
EWBJDF8FM6386VPD
accept-ranges
bytes
abp
29
content-length
17120
server
nginx
x-amz-server-side-encryption
AES256
fastly-io-info
ifsz=18050 idim=800x450 ifmt=jpeg ofsz=19906 odim=880x550 ofmt=jpeg
x-fastly-object-storage
false
x-debug
/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_550%2Cw_880%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/http%3A//cdn.taboola.com/libtrc/static/thumbnails/b61de851db2c8b443fe543ebd957d14b.jpg
date
Sun, 06 Sep 2026 19:15:30 GMT
x-served-by
cache-iad-kiad7000049-IAD, cache-iad-kiad7000049-IAD, cache-iad-kcgs7200125-IAD, cache-nyc-kteb1890043-NYC, cache-iad-kcgs7200158-IAD, cache-lon4258-LON
vary
ImageFormat
x-amz-id-2
SXULjYB9561EQvsT7AVjWtE3S6eBmYHkcCFeJHqQiZBvKyl+CFy2C2zv9bT+Jh/M/Tsl7n9e3wdsSLVL2RQUo8gCVzGUW/nA
x-vcl-version
53
x-vcl-time-ms
77
via
1.1 varnish, 1.1 varnish
x-ratelimit-remaining
100
access-control-allow-origin
*
req-referer
https://www.firstcoastnews.com/
fastly-io-served-by
img24-us-east4
x-ratelimit-limit
101
fastly-io-transform-stats
ifsz=18050 ofsz=19906 ofmt=jpeg
GET
H2
200
19732673_082526-cc-abcn-trump-military-deportation-video.jpg%3Fw%3D1600
images.taboola.com/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_550%2Cw_880%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.abcotvs.com/dip/images/
34 KB
35 KB
118ms
117ms
Image
image/webp
151.101.193.44
Fastly
General
Full URL
https://images.taboola.com/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_550%2Cw_880%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.abcotvs.com/dip/images/19732673_082526-cc-abcn-trump-military-deportation-video.jpg%3Fw%3D1600
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
nginx /
Resource Hash
c21680ada51a0814474a2964a95259a9405834011154ac84a0aa8a8c7e35c09e
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
4977ee73f7cc0a387557c5e3270a17c5
access-control-expose-headers
Content-Length,ETag,Server-Timing,X-Content-Type-Options
etag
"fRFffuar5L8bCkf0HVaIskZzZCKESdV7kuzDmaP37go"
age
319192
x-content-type-options
nosniff
server-timing
cld-fastly;mitm=fa;dur=3;cpu=1;start=2026-09-03T02:35:38.430Z;desc=hit,rtt;dur=0,content-info;desc="width=1500,height=900,bytes=105860,format=\"jpg\",owidth=1600,oheight=900,obytes=580092,oformat=\"jpg\",crt=1787657569,ocrt=1787657157,ef=(1,13,17,23,30)"
x-cache
MISS, HIT, HIT
content-type
image/webp
x-cache-hits
0, 17, 0
cache-control
public, max-age=31536000
x-envoy-upstream-service-time
451
x-timer
S1788722131.579666,VS0,VE1
x-tbl-io-backend
cloudinary-fastly-fallback
x-ratelimit-reset
1
accept-ranges
bytes
content-length
35008
server
nginx
fastly-io-info
ifsz=105860 idim=1500x900 ifmt=jpeg ofsz=110369 odim=1500x900 ofmt=jpeg
x-debug
/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_550%2Cw_880%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.abcotvs.com/dip/images/19732673_082526-cc-abcn-trump-military-deportation-video.jpg%3Fw%3D1600
date
Sun, 06 Sep 2026 19:15:30 GMT
x-served-by
cache-iad-kiad7000133-IAD, cache-iad-kcgs7200052-IAD, cache-lon4258-LON
vary
ImageFormat
x-vcl-version
53
timing-allow-origin
*
x-vcl-time-ms
1
expiration
expiry-date="Fri, 25 Sep 2026 00:00:00 GMT", rule-id="delete fetch for taboola-fastly after 30 days"
via
1.1 varnish, 1.1 varnish
x-ratelimit-remaining
100
x-tbl-io-error
fastly_io_error_400_Bad Request
access-control-allow-origin
*
req-referer
https://abc30.com/
fastly-io-served-by
img02-us-east4
x-ratelimit-limit
101
fastly-io-transform-stats
ifsz=105860 ofsz=110369 ofmt=jpeg
GET
H2
200
19774488_090126-kabc-4am-lb-transformer-chase-2-vid.jpg%3Fw%3D1600
images.taboola.com/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_550%2Cw_880%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.abcotvs.com/dip/images/
61 KB
62 KB
126ms
124ms
Image
image/webp
151.101.193.44
Fastly
General
Full URL
https://images.taboola.com/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_550%2Cw_880%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.abcotvs.com/dip/images/19774488_090126-kabc-4am-lb-transformer-chase-2-vid.jpg%3Fw%3D1600
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
nginx /
Resource Hash
931b8bbc3f00ce6662ae84004b4aaf4436edeabdaba41ab83985df1a014a4366
Security Headers
Name Value
Strict-Transport-Security max-age=604800
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
995e6ae54fa8470ccb63f1d13ec4a446
access-control-expose-headers
Content-Length,ETag,Server-Timing,X-Content-Type-Options
etag
"9LEGRqO+daXpH29YTpX3wBRvpEqSIgYT3X41+w9HSZg"
age
457402
x-content-type-options
nosniff
server-timing
cld-fastly;mitm=fa;dur=955;cpu=1;start=2026-09-01T12:12:06.981Z;desc=miss,rtt;dur=0,content-info;desc="width=1500,height=900,bytes=153545,format=\"jpg\",owidth=1600,oheight=900,obytes=692560,oformat=\"jpg\",crt=1788264727,ocrt=1788264727,ef=(1,13,17,23,30)",cloudinary;dur=930;start=2026-09-01T12:12:06.992Z,cld-id;desc=995e6ae54fa8470ccb63f1d13ec4a446
x-cache
HIT, MISS, HIT, HIT
content-type
image/webp
x-cache-hits
4, 0, 54, 0
cache-control
public, max-age=31536000
x-envoy-upstream-service-time
318
x-timer
S1788722131.583512,VS0,VE7
x-tbl-io-backend
fastly
x-ratelimit-reset
1
accept-ranges
bytes
content-length
62368
server
nginx
fastly-io-info
ifsz=153545 idim=1500x900 ifmt=jpeg ofsz=118400 odim=1500x900 ofmt=jpeg
x-debug
/taboola/image/fetch/f_jpg%2Cq_auto%2Ch_550%2Cw_880%2Cc_fill%2Cg_faces:auto%2Ce_sharpen/https%3A//cdn.abcotvs.com/dip/images/19774488_090126-kabc-4am-lb-transformer-chase-2-vid.jpg%3Fw%3D1600
date
Sun, 06 Sep 2026 19:15:30 GMT
x-served-by
cache-iad-kcgs7200072-IAD, cache-lax-kwhp1940069-LAX, cache-iad-kcgs7200141-IAD, cache-lon4258-LON
vary
ImageFormat
strict-transport-security
max-age=604800
x-vcl-version
53
timing-allow-origin
*
x-vcl-time-ms
7
via
1.1 varnish, 1.1 varnish
x-ratelimit-remaining
100
access-control-allow-origin
*
req-referer
https://abc7.com/
fastly-io-served-by
img04-us-east4
x-ratelimit-limit
101
fastly-io-transform-stats
ifsz=153545 ofsz=118400 ofmt=jpeg
GET
H2
200
ping
ping.chartbeat.net/
43 B
200 B
189ms
189ms
Image
image/gif
3.221.141.84
Amazon.com
General
Full URL
https://ping.chartbeat.net/ping?h=abc7.com&p=%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F&u=9bQN7CvU_-YCS53kA&d=abc7.com&g=23214&g0=No%20Section&g1=ABC7.COM%20STAFF&g7=1788359393000&n=1&f=00001&c=0.02&x=0&m=0&y=7412&o=1600&w=1200&j=30&R=1&W=0&I=0&E=1&e=1&r=&PA=https%3A%2F%2Fabc7.com%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F&b=1990&t=BlccMaBy-WlwBFGG2FBnUk3WmSeKK&V=152&tz=-180&_acct=paid&sn=2&sv=BpY6fNCXsoJQBnNB2kDkdAbtiBDis&sr=external&sd=1&im=067b0fff&_
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.221.141.84 Ashburn, United States, ASN14618 (AMAZON-AES - Amazon.com, Inc., US),
Reverse DNS
ec2-3-221-141-84.compute-1.amazonaws.com
Software
/
Resource Hash
cf4724b2f736ed1a0ae6bc28f1ead963d9cd2c1fd87b6ef32e7799fc1c5c8bda

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

expires
0
cache-control
no-cache, no-store, must-revalidate
content-length
43
date
Sun, 06 Sep 2026 19:15:30 GMT
pragma
no-cache
content-type
image/gif
cross-origin-resource-policy
cross-origin
GET
H2
200
id Show response
sw88.go.com/
48 B
450 B
364ms
113ms
XHR
application/x-javascript
63.140.62.210
Amazon.com
General
Full URL
https://sw88.go.com/id?d_visid_ver=5.5.0&d_fieldgroup=A&mcorgid=19916ABB53224B2C0A490D45%40AdobeOrg&mid=54109714201665181872321563256462948945&d_coppa=true&ts=1788722130302
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
63.140.62.210 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ip-63-140-62-210.data.adobedc.net
Software
jag /
Resource Hash
48eca4f55bdb07e7dc2d07e3773dbd8691736ac074f0fcbae00ca3f9b93a0c39
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
Content-Type
application/x-www-form-urlencoded
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
no-cache, no-store, max-age=0, no-transform, private
access-control-allow-credentials
true
x-content-type-options
nosniff
access-control-allow-origin
https://abc7.com
p3p
CP="This is not a P3P policy"
content-length
48
date
Sun, 06 Sep 2026 19:15:30 GMT
x-xss-protection
1; mode=block
content-type
application/x-javascript;charset=utf-8
vary
Origin
server
jag
GET
H2
200
de38fa60eef746e1.css
login.disney.com/_next/static/css/ Frame 4730
219 KB
32 KB
130ms
128ms
Stylesheet
text/css
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/css/de38fa60eef746e1.css?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
d76ef0c6e94d23d32a07872f721d63d3775fe20958b1ba3f4e2b179b05ee57f5

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
f51f2b3757bda138370ebd6caba9aef5
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"36cc4-1a01fc3c5d8"
age
1473340
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
QrNt1XwQwaMoGHu4DC2fjKCT5IIjjbGaa_adL2qgjxPuB-M8YzXL1Q==
date
Thu, 20 Aug 2026 17:59:50 GMT
content-type
text/css; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
d8901c280c38085c.css
login.disney.com/_next/static/css/ Frame 4730
6 KB
2 KB
155ms
153ms
Stylesheet
text/css
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/css/d8901c280c38085c.css?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
73885c6f8a0e282f7e11106b5afa4177f67cf2e7ebe19b626b7efa3ea7cab50a

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
0f4ef83617851f1c7f0eeea05d9e6558
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"18d1-1a01fc3c5d8"
age
1473340
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
yyV4pUyec5TOygiYbUHjN8glJFjWIfoPQpLqxONGE_JKz-z5niWpUg==
date
Thu, 20 Aug 2026 17:59:50 GMT
content-type
text/css; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
e4a06624fb137980.css
login.disney.com/_next/static/css/ Frame 4730
1 KB
964 B
155ms
154ms
Stylesheet
text/css
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/css/e4a06624fb137980.css?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
64588e9366369ac597537cac9d9c97aad90ef18b4037dbb4ec21ac910266a4a9

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
4a9815e94e75d17d68c04a0430ab4d6e
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"5b8-1a01fc3c5d8"
age
1473340
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
2NzxmjC8o-tqAnkXsKt3izDAa-Hqx9V9G7aq97UrnRwmjaUFbBK_7w==
date
Thu, 20 Aug 2026 17:59:50 GMT
content-type
text/css; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
webpack-1c192558414fa53c.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
5 KB
3 KB
134ms
127ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
80498a3ab72aa96861f15ab3c5b446a8c64886e23cab0078f7c588340f9305b1

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
416d48e74db1536d5d359dd9ddb85d7f
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"1219-1a068706318"
age
253646
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
6A28jirdwV0A_8obPhT7GkRxdR-RjNzxFE_rhsg7i7jhqPbVa41tKQ==
date
Thu, 03 Sep 2026 20:48:04 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 03 Sep 2026 18:03:11 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
fd9d1056-9e1c49e7e597db6b.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
169 KB
53 KB
120ms
113ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/fd9d1056-9e1c49e7e597db6b.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
865cad64a44a0c49b5bdadd6c3e9a9a363f6943fb9a70efc1b6292ebab67276f

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
f882da6551ec120432754bf37b8571ae
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"2a325-1a01fc3c5d8"
age
1473339
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
WWdhFCMxgs8aC96oAWLmdTOQPQLRRbB6EXoLETqDp5hyCoxRAktXEA==
date
Thu, 20 Aug 2026 17:59:51 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
2117-a790118259d114bc.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
122 KB
32 KB
138ms
132ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/2117-a790118259d114bc.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
0c487c17a7fc63c340cea7a4f760d4405984ffb7283af39a684bd421a1306f66

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
2d64b1401fd67acabf1e3a7b9980ce78
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"1e901-1a068706318"
age
253646
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
swlKR6aJWNLNYpU0qK1_6Q-1_3D7oag_X16N5dspjaLezoU31qGiVg==
date
Thu, 03 Sep 2026 20:48:04 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 03 Sep 2026 18:03:11 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
main-app-5294d1645fe5526e.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
471 B
661 B
144ms
138ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/main-app-5294d1645fe5526e.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
5fbb88ecc6a5304feeb23c35a7f6115c70df5f741f69d447369cc8ab41590473

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
4f702e6b938f581337e98242b52810ef
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"1d7-1a01fc3c5d8"
age
1473340
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
ZJ0cuKZFjI_BUroT-otkDBkECoUMFGVvWdJ5XZyOzn_UjgOpUvhJ7w==
date
Thu, 20 Aug 2026 17:59:50 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding,Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
5502-cc26cd2cc9324d08.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
8 KB
3 KB
145ms
139ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/5502-cc26cd2cc9324d08.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
f760472538d822f54578f528f66687dbe80ed9d827f9691e8a7a0f7913603354

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
084befe732272dd11f9c967cce15f430
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"2008-1a01fc3c5d8"
age
1473340
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
Rire_WICU5FJK7D_9DjL0PKkvxFwfKIDGTpNOVrfho9t2hBIZSyc9A==
date
Thu, 20 Aug 2026 17:59:50 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
4170-dd4027ed6752dacf.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
470 KB
138 KB
149ms
144ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/4170-dd4027ed6752dacf.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
cc789e331fb3deb89e11e739ccd76e76294209f85836efba69721761130b89a3

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
fd08ceb2ea33df28c5d9cd84ec17299d
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"759df-1a01fc3c5d8"
age
1473339
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
QsRozBcrZswRuxjnoIp-ZXY2jmsKwtfv08OcX3_OtEMhX6LIQ5nuhg==
date
Thu, 20 Aug 2026 17:59:51 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
1396-3f279983932d93c6.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
12 KB
4 KB
208ms
202ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/1396-3f279983932d93c6.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
d0c73256001ad05049f988f60029c4fce65ea97228ca0bb8277c720ec4f8b99c

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
c438ebb590a739dcc51437b112c71782
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"2e5f-1a049b6dce0"
age
771906
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
vFoTSHKqPrHFzY_xMVwdbbdeJoRFjgU-9MmyVkOw_k6HKM-I_MG8jg==
date
Fri, 28 Aug 2026 20:50:24 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Fri, 28 Aug 2026 18:51:56 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
2972-b9f128ed67f4ebb8.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
26 KB
9 KB
210ms
205ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/2972-b9f128ed67f4ebb8.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
6e502a26091acaa438e2968708f1c772eb06b83feb401adcaec76ef0cc1d0fd4

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
6f112a71e6b2c1cffeb4c5ca89efc507
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"6608-1a01fc3c5d8"
age
1473340
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
Dt7tgcZoFG5AcD9CjV8tmKySEuOl6ch3J4FlJWJEaNfBNKjxBFX-LA==
date
Thu, 20 Aug 2026 17:59:50 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
3847-45a8a3029d78b66b.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
10 KB
5 KB
212ms
207ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/3847-45a8a3029d78b66b.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
2b3365310bcea096bf4e32ae074cea8eedd41be347517a28af8dab221337f326

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
166b48203149658a35d8603fc2faa9eb
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"264f-1a01fc3c5d8"
age
1473340
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
Inkp-7x7Pnwe4O_OY3l8G_WGzViywJAZ4Fy3oz8Qr2JMdTEhgrGrag==
date
Thu, 20 Aug 2026 17:59:50 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
958-66742d7303f0c1c4.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
53 KB
12 KB
214ms
209ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/958-66742d7303f0c1c4.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
32b4b6f740d48f40d78e2618dd5225090e802f02c6c761ba6c7a0aea19f9d792

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
2dcb096d7c54a0275ee4b7e3f19070b2
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"d286-1a068706318"
age
253646
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
JQLFPzfz67VUWLgeVP0nAVM7bkV3pu-lb3dswTq5kQchLf-kWrHT3Q==
date
Thu, 03 Sep 2026 20:48:04 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 03 Sep 2026 18:03:11 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
6750-98926c73b3d213f3.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
38 KB
10 KB
217ms
212ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/6750-98926c73b3d213f3.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
cd964287a1460f7757f5902c2789a03beda47f271f23a710f1712b138e17d3ad

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
e50c951d4b0f7ae8ce6ccc87a25f19e1
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"970e-1a068706318"
age
253880
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
MYvZbEnjvZskdXqn0Wz_gZswa5qX6CiYoxzu7LfS4XNAKWEHfrZkWw==
date
Thu, 03 Sep 2026 20:44:10 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 03 Sep 2026 18:03:11 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
6540-fc8e03091efbb1c6.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
23 KB
7 KB
218ms
214ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/6540-fc8e03091efbb1c6.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
c60dd56fa89a54dec16f59032a146d691629bc948375377cd1633805f6045c52

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
7034f1de25506027f0130e232c3efeb4
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"5ddd-1a05f957328"
age
266666
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
PaY9sRk0_0ID2Z5ZWJRYI6o-nAGBdcTxfGc_oyhJCyBI8O6uvm5_eg==
date
Thu, 03 Sep 2026 17:11:04 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
page-90ef9a5d43c8e288.js Show response
login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/v5/bridge/web/ Frame 4730
15 KB
6 KB
220ms
216ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/v5/bridge/web/page-90ef9a5d43c8e288.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
f12a31a08542c59f49e60c0ee95cb037b3fcb193e7d47b6cef8022b04679c856

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
1916510a78e2ca25b49e5ae4ae21a779
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"3ad3-1a05f957328"
age
266966
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
VRz3FIRbtPS_fXN2V509XtBBUQkgre3QcH3iWPDrRFH0pnSwjXY76g==
date
Thu, 03 Sep 2026 17:06:04 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
global-error-6e887188deb04cb3.js Show response
login.disney.com/_next/static/chunks/app/ Frame 4730
16 KB
8 KB
226ms
221ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/app/global-error-6e887188deb04cb3.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
f7549e1af0226633fb103b2cfa32ab09da00ef6c5481e20d7aceb7f5d802d81e

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
50e8ad8211868abf3810546659f6fe82
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"3e76-1a049b6dce0"
age
772075
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
akoZVdBuruPZ_MH0racEuOrmCBxh__Ys1zIrMCQkuVXkNo3S751dtQ==
date
Fri, 28 Aug 2026 20:47:35 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Fri, 28 Aug 2026 18:51:56 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
3002-da83019d19c66d43.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
12 KB
5 KB
226ms
222ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/3002-da83019d19c66d43.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
b1124899032e38d02f08b05e65e503d82bb725cea86fe3522d47d772f2e2bb9a

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
367dc7b9ff65f4b408044ca8abfcba0d
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"2faa-1a049b6dce0"
age
772178
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
pWHfE89Qn_TWOMGb5q98Q6s6E5MXfuCsmosC2YfaeRsqL89nemokHg==
date
Fri, 28 Aug 2026 20:45:52 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Fri, 28 Aug 2026 18:51:56 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
layout-c885c4431cbc19af.js Show response
login.disney.com/_next/static/chunks/app/ Frame 4730
22 KB
11 KB
228ms
224ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/app/layout-c885c4431cbc19af.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
15fcb37ad1841a648ebc49e07a4de1ac27eb723f3c046134f9b6aee1be1b7029

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
e6ffaed439bc075b02db304ccf11182c
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"5770-1a068706318"
age
253646
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
hBWHI52G240iEXSP9OhllCqa49vUPOMuGiLESNxNEsMLIDfI79SAFg==
date
Thu, 03 Sep 2026 20:48:04 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 03 Sep 2026 18:03:11 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
6188-2929cb20df4f57cc.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
36 KB
14 KB
234ms
230ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/6188-2929cb20df4f57cc.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
274246e8fb7a655c0966419e322cd64147009dacb6dc6e82a1329492488fcc03

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
4c99f635ad81266dd79fcd67ddf074bd
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"8f4a-1a01fc3c5d8"
age
1473339
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
cUaUmvaGNT2wWR6a2Z3-Dx2HF_KdmWze1aNUyBLjRfjZvXkCnmzEIw==
date
Thu, 20 Aug 2026 17:59:51 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
1839-c2cf34b7e53925bf.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
5 KB
2 KB
228ms
224ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/1839-c2cf34b7e53925bf.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
fef2d069ceea4b17b00cb2ca255669a0f79fc2bfc65cb5b943e645f0fb1d8c5f

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
06cca400408e89b59f68faf83c13f803
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"13ec-1a01fc3c5d8"
age
1473339
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
23rhFy_vDvIlSFkhoHAfcSS0eNgxdoeiOogB4CA_Fs-sp8Lc9RcnFA==
date
Thu, 20 Aug 2026 17:59:51 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
6485-92fc71690688d2da.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
24 KB
11 KB
229ms
226ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/6485-92fc71690688d2da.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
20896db2d807b7482e8bc79ea86da350745171495bcac31012c6dd9e94c9eb33

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
093621680b0861803d9e29b91fa6df61
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"60ef-1a05f957328"
age
266791
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
atyydUP0jMv3UDMkTZ0q5sqaIAIdgsoPEXMSAU-OWISFg91X120l6g==
date
Thu, 03 Sep 2026 17:08:58 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
4728-28ec01fc97a8da09.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
9 KB
4 KB
230ms
227ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/4728-28ec01fc97a8da09.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
4e9589b1b6233a9ee58b38e96c1ae1e73a7b034e622cce2b9a0817f64cf36e7d

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
3310ebf2373d3b8a808c6e070e5e56de
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"2493-1a05f957328"
age
266797
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
SAsY0Xk_4Cniy3dgJElAaFbt3NfT5TvtL6Poh5rKIWeOzULKab0OPQ==
date
Thu, 03 Sep 2026 17:08:53 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
layout-4f7430b740d86c86.js Show response
login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/v5/bridge/ Frame 4730
1 KB
1 KB
230ms
227ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/v5/bridge/layout-4f7430b740d86c86.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
e878ed2e68c901d83b844539e3977ba51532345bc9503b18bb31e545d4e0f425

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
291fc6d5e7bdf432cdd76a8708207274
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"4ed-1a05f957328"
age
266797
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
svwvCy9QCRBT1XgpEF5UqW4Nb8VIo690QKak7UFEX9a8vkJ-Qqfw2A==
date
Thu, 03 Sep 2026 17:08:53 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
8667-b2c669368225b0b5.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
6 KB
3 KB
233ms
229ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/8667-b2c669368225b0b5.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
38458430b8c047aff1318c2085ae0cf8fbd697b244577ecf39ad03922e121991

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
952a6e760c5a2c500d1ee0b256e8d4a5
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"18f3-1a01fc3c5d8"
age
1473339
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
b_ByfYEW6J46NzyPHxuPq8dp1hYFV4UMYW1bydcjtHVyw29FwS2HuQ==
date
Thu, 20 Aug 2026 17:59:51 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
6086-188167ceda679c0d.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
9 KB
4 KB
234ms
231ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/6086-188167ceda679c0d.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
41edead752df35287cb29dea400d517b2c3045fdd3fdfd15e437179ff2e0590d

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
e6192a5b90ec9b3b58cf2353b80ead27
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"259a-1a049b6dce0"
age
771878
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
W2h2-UUaAPqX6VzNyQYnJBI4wgmWXUsfTKHwTjsN2YPfUI4epRDPiQ==
date
Fri, 28 Aug 2026 20:50:52 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Fri, 28 Aug 2026 18:51:56 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
not-found-08af5c64b0c22b74.js Show response
login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/ Frame 4730
182 B
610 B
238ms
235ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/not-found-08af5c64b0c22b74.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
83ae9a0ef5410d10b57b5382c2e0c8d2540749902b0b8eead9eb170d9cab2bd4

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
cfb479f9b50f063ed666d9e1ec291db6
cache-control
public, max-age=31536000, immutable
etag
W/"b6-1a049b6dce0"
age
771878
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
content-length
182
x-amz-cf-id
_bRsz9tthkZdRwqxyHSmqFRjfzHIDJ-0H0OyYnP5sMeouhXnjfVHGw==
date
Fri, 28 Aug 2026 20:50:52 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Fri, 28 Aug 2026 18:51:56 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
6436-70d95a909f8d6fe0.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
4 KB
2 KB
234ms
231ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/6436-70d95a909f8d6fe0.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
fb91aecea9a760cd50e60eb0017a72162457414778aa639ee2cfefb8bb9d4a95

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
09a266ba67b601e3678f05a5d8c088d2
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"10f4-1a01fc3c5d8"
age
1473340
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
X7UZ5nzjTxqrc5xYCDNX9va2JBNMjHlQ5Yq9jVfHmhMVVALkLl8I_g==
date
Thu, 20 Aug 2026 17:59:50 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
error-80985caa7e15c56d.js Show response
login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/ Frame 4730
22 KB
9 KB
236ms
233ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/error-80985caa7e15c56d.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
a46359e33c619aea75577a13e3a7d789a9d448045b262ecfffd3a838e5b155be

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
0aa340d5b9cda2c7944968e360356aaa
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"59a5-1a05f957328"
age
266966
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
2IgwR9Wz9MTSD2rThw0YOrKzitfMwY8TCwvZh8l7qqrQhs0reGSEsA==
date
Thu, 03 Sep 2026 17:06:04 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
l10n.js Show response
login.disney.com/en-US/US/DATG-OTV.KABC.WEB/ Frame 4730
510 KB
77 KB
177ms
176ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/l10n.js
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
b98910052a35e717266061c19a4c04fe0398d939cd096a7c3a61bd44657ef727

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
cfe2f1d9e7cf19d8f2f86230302b444e
cache-control
public, s-maxage=900, max-age=0, must-revalidate, stale-while-revalidate=60, stale-if-error=900, public, max-age=21600, stale-while-revalidate=86400, stale-if-error=86400
content-encoding
gzip
age
631
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
R0ZwH1u7KdRNwVDFldgx8kKOLd7fZufPqbRE82GKOSOEdlsQgeNlfw==
date
Sun, 06 Sep 2026 19:04:59 GMT
content-type
application/javascript; charset=utf-8
vary
Accept-Encoding,RSC
x-amz-cf-pop
FRA56-P10
GET
H2
200
siteconfig.js Show response
login.disney.com/en-US/US/DATG-OTV.KABC.WEB/ Frame 4730
24 KB
6 KB
244ms
243ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/siteconfig.js
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
428a4999f41763e30da3413947d7fc44dc8aa24339b219c1bd685c5d6f83783b

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
5a6412313d4c00c98605eb472dc37df8
cache-control
public, s-maxage=900, max-age=0, must-revalidate, stale-while-revalidate=60, stale-if-error=900, public, max-age=21600, stale-while-revalidate=86400, stale-if-error=86400
content-encoding
gzip
age
254
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
SFY3-a_F6__GP5lbfvcMKqZzPorpBi5tT81EwB8H5x6rruYzKYYaRQ==
date
Sun, 06 Sep 2026 19:11:16 GMT
content-type
application/javascript; charset=utf-8
vary
Accept-Encoding,RSC
x-amz-cf-pop
FRA56-P10
GET
H3
200
enterprise.js Show response
www.google.com/recaptcha/ Frame 4730
2 KB
1 KB
244ms
126ms
Script
text/javascript
142.251.150.119
Google LLC
General
Full URL
https://www.google.com/recaptcha/enterprise.js?render=6LcnzusZAAAAABiX7zUG2lN9BBH_1ERH1pfyR95-
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.150.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
0de1f60cc82ae7981ee7915d7151eccfa77257033740a99b143581132d8e96a5
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
private, max-age=300
content-encoding
gzip
cross-origin-resource-policy
cross-origin
report-to
{"group":"coop_38fac9d5b82543fc4729580d18ff2d3d","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/38fac9d5b82543fc4729580d18ff2d3d"}]}
x-content-type-options
nosniff
expires
Sun, 06 Sep 2026 19:15:30 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cross-origin-opener-policy-report-only
same-origin; report-to="coop_38fac9d5b82543fc4729580d18ff2d3d"
date
Sun, 06 Sep 2026 19:15:30 GMT
x-xss-protection
0
content-type
text/javascript; charset=utf-8
server
ESF
x-frame-options
SAMEORIGIN
GET
H2
200
bounce
ib.adnxs.com/ Frame D03C
Redirect Chain
  • https://ib.adnxs.com/setuid?entity=584&code=419acdb7-b09e-4b32-b034-56c31d5fd705-tuct11974151&gdpr=0&gdpr_consent=
  • https://ib.adnxs.com/bounce?%2Fsetuid%3Fentity%3D584%26code%3D419acdb7-b09e-4b32-b034-56c31d5fd705-tuct11974151%26gdpr%3D0%26gdpr_consent%3D
43 B
1 KB
139ms
139ms
Image
image/gif
4.208.245.100
Microsoft Corpora...
General
Full URL
https://ib.adnxs.com/bounce?%2Fsetuid%3Fentity%3D584%26code%3D419acdb7-b09e-4b32-b034-56c31d5fd705-tuct11974151%26gdpr%3D0%26gdpr_consent%3D
Protocol
H2
Server
4.208.245.100 Dublin, Ireland, ASN8075 (MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation, US),
Reverse DNS
Software
nginx/1.25.5 /
Resource Hash
4b5b6b15c6255109e06720cce42a06d3aead8b7874423d9c52cb0303212c25ef
Security Headers
Name Value
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
Referer

Response headers

cache-control
no-store, no-cache, private
pragma
no-cache
accept-ch
Sec-CH-UA-Full-Version-List,Sec-CH-UA-Arch,Sec-CH-UA-Model,Sec-CH-UA-Platform-Version,Sec-CH-UA-Bitness
access-control-allow-credentials
true
x-proxy-origin
187.15.128.65; 187.15.128.65; 1529.nginx-loadbalancer.mgmt.zne1.xandr-xc.net; *.adnxs.com
expires
Sat, 15 Nov 2008 16:00:00 GMT
access-control-allow-origin
*
an-x-request-uuid
08d68b0c-b2d6-4fa1-aea1-2d764b3a59af
content-length
43
p3p
policyref="http://cdn.adnxs-simple.com/w3c/policy/p3p.xml", CP="NOI DSP COR ADM PSAo PSDo OURo SAMo UNRo OTRo BUS COM NAV DEM STA PRE"
date
Sun, 06 Sep 2026 19:15:30 GMT
x-xss-protection
0
content-type
image/gif
server
nginx/1.25.5

Redirect headers

cache-control
no-store, no-cache, private
location
https://ib.adnxs.com/bounce?%2Fsetuid%3Fentity%3D584%26code%3D419acdb7-b09e-4b32-b034-56c31d5fd705-tuct11974151%26gdpr%3D0%26gdpr_consent%3D
pragma
no-cache
accept-ch
Sec-CH-UA-Full-Version-List,Sec-CH-UA-Arch,Sec-CH-UA-Model,Sec-CH-UA-Platform-Version,Sec-CH-UA-Bitness
x-proxy-origin
187.15.128.65; 187.15.128.65; 1529.nginx-loadbalancer.mgmt.zne1.xandr-xc.net; *.adnxs.com
expires
Sat, 15 Nov 2008 16:00:00 GMT
an-x-request-uuid
f0dbd5e2-a578-412d-ac76-ec48f462c9f1
content-length
0
p3p
policyref="http://cdn.adnxs-simple.com/w3c/policy/p3p.xml", CP="NOI DSP COR ADM PSAo PSDo OURo SAMo UNRo OTRo BUS COM NAV DEM STA PRE"
date
Sun, 06 Sep 2026 19:15:30 GMT
x-xss-protection
0
content-type
text/html; charset=utf-8
server
nginx/1.25.5
GET
H2
200
um
trc.taboola.com/sg/google-authorized-buyers/1/ Frame D03C
Redirect Chain
  • https://cm.g.doubleclick.net/pixel?google_nid=realize&google_hm=NDE5YWNkYjctYjA5ZS00YjMyLWIwMzQtNTZjMzFkNWZkNzA1LXR1Y3QxMTk3NDE1MQ&google_cm&&gdpr=0&gdpr_consent=&ui=419acdb7-b09e-4b32-b034-56c31d5...
  • https://cm.g.doubleclick.net/pixel?google_nid=realize&google_hm=NDE5YWNkYjctYjA5ZS00YjMyLWIwMzQtNTZjMzFkNWZkNzA1LXR1Y3QxMTk3NDE1MQ&google_cm=&gdpr=0&gdpr_consent=&ui=419acdb7-b09e-4b32-b034-56c31d5...
  • https://trc.taboola.com/sg/google-authorized-buyers/1/um?gdpr=0&gdpr_consent=&ui=419acdb7-b09e-4b32-b034-56c31d5fd705-tuct11974151&google_gid=CAESED3a9cgUGsYhC81Z3AzTpUE&google_cver=1
43 B
367 B
192ms
191ms
Image
image/gif
151.101.193.44
Fastly
General
Full URL
https://trc.taboola.com/sg/google-authorized-buyers/1/um?gdpr=0&gdpr_consent=&ui=419acdb7-b09e-4b32-b034-56c31d5fd705-tuct11974151&google_gid=CAESED3a9cgUGsYhC81Z3AzTpUE&google_cver=1
Protocol
H2
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
nginx /
Resource Hash
0d9762a1a60deef8aa093c473ad27c38eed77184d6940e7df06d89d77cbd3e94

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
Referer

Response headers

x-cache
MISS
p3p
policyref="http://trc.taboola.com/p3p.xml", CP="NOI DSP COR LAW NID CURa ADMa DEVa PSAa PSDa OUR BUS IND UNI COM NAV INT DEM"
date
Sun, 06 Sep 2026 19:15:31 GMT
x-served-by
cache-lon4258-LON
x-cache-hits
0
cache-control
no-cache, no-store
x-fastly-to-nlb-rtt
73746
pragma
no-cache
x-timer
S1788722131.973197,VS0,VE75
x-vcl-time-ms
75
access-control-allow-credentials
true
via
1.1 varnish
accept-ranges
bytes
access-control-allow-origin
*
x-service-version
v1
server
nginx

Redirect headers

cache-control
no-cache, must-revalidate
location
https://trc.taboola.com/sg/google-authorized-buyers/1/um?gdpr=0&gdpr_consent=&ui=419acdb7-b09e-4b32-b034-56c31d5fd705-tuct11974151&google_gid=CAESED3a9cgUGsYhC81Z3AzTpUE&google_cver=1
pragma
no-cache
cross-origin-resource-policy
cross-origin
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
content-length
396
date
Sun, 06 Sep 2026 19:15:30 GMT
x-xss-protection
0
content-type
text/html; charset=UTF-8
server
HTTP server (unknown)
OPTIONS
H2
204
/
sdk.iad-05.braze.com/api/v3/data/ Frame
0
0
491ms
225ms
Preflight
104.18.38.107
Cloudflare
General
Full URL
https://sdk.iad-05.braze.com/api/v3/data/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.18.38.107 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

Accept
*/*
Access-Control-Request-Headers
content-type,x-braze-api-key,x-braze-datarequest,x-braze-last-req-ms-ago,x-braze-req-attempt,x-braze-triggersrequest,x-requested-with
Access-Control-Request-Method
POST
Origin
https://abc7.com
Sec-Fetch-Mode
cors
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36

Response headers

access-control-allow-headers
*
access-control-allow-methods
POST, OPTIONS
access-control-allow-origin
*
cf-cache-status
DYNAMIC
cf-ray
a36fcd84af64e86b-FRA
date
Sun, 06 Sep 2026 19:15:30 GMT
server
cloudflare
strict-transport-security
max-age=31536000; includeSubDomains
vary
Origin
POST
H2
201
/ Show response
sdk.iad-05.braze.com/api/v3/data/
642 B
463 B
337ms
336ms
XHR
application/json
104.18.38.107
Cloudflare
General
Full URL
https://sdk.iad-05.braze.com/api/v3/data/
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.18.38.107 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
32f8b521982aee4f015985c4270e3b0a2731ac7c3d075ee094c463ec6b7ab23c
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
X-Braze-TriggersRequest
true
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
X-Braze-Last-Req-Ms-Ago
7200000
X-Braze-DataRequest
true
sec-ch-ua-mobile
?0
X-Braze-Req-Attempt
1
X-Requested-With
XMLHttpRequest
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
Content-type
application/json
X-Braze-Api-Key
10187d86-76ca-4351-a1ca-d70429bc4589

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
content-encoding
gzip
cf-cache-status
DYNAMIC
x-ratelimit-reset
1788722133
access-control-allow-methods
POST, OPTIONS
cf-ray
a36fcd861c63e86b-FRA
x-ratelimit-remaining
499
x-ratelimit-period
3
access-control-allow-origin
*
date
Sun, 06 Sep 2026 19:15:31 GMT
x-ratelimit-limit
500
content-type
application/json; charset=utf-8
vary
Origin, Accept-Encoding
server
cloudflare
access-control-allow-headers
*
POST
H2
201
/ Show response
sdk.iad-05.braze.com/api/v3/data/
652 B
597 B
233ms
231ms
XHR
application/json
104.18.38.107
Cloudflare
General
Full URL
https://sdk.iad-05.braze.com/api/v3/data/
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.18.38.107 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
8ae4d0381d7712cd0bb3759a3c6b1299bcf2dc7a4090d56dfd62ea8532b199d2
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
X-Braze-Last-Req-Ms-Ago
7200000
sec-ch-ua-mobile
?0
X-Braze-Req-Attempt
1
X-Braze-Req-Tokens-Remaining
29
X-Requested-With
XMLHttpRequest
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
Content-type
application/json
X-Braze-Api-Key
10187d86-76ca-4351-a1ca-d70429bc4589

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
content-encoding
gzip
cf-cache-status
DYNAMIC
x-ratelimit-reset
1788722133
access-control-allow-methods
POST, OPTIONS
cf-ray
a36fcd861c5ae86b-FRA
x-ratelimit-remaining
985
x-ratelimit-period
3
access-control-allow-origin
*
date
Sun, 06 Sep 2026 19:15:31 GMT
x-ratelimit-limit
986
content-type
application/json; charset=utf-8
vary
Origin, Accept-Encoding
server
cloudflare
access-control-allow-headers
*
OPTIONS
H2
204
/
sdk.iad-05.braze.com/api/v3/data/ Frame
0
0
490ms
225ms
Preflight
104.18.38.107
Cloudflare
General
Full URL
https://sdk.iad-05.braze.com/api/v3/data/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.18.38.107 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

Accept
*/*
Access-Control-Request-Headers
content-type,x-braze-api-key,x-braze-last-req-ms-ago,x-braze-req-attempt,x-braze-req-tokens-remaining,x-requested-with
Access-Control-Request-Method
POST
Origin
https://abc7.com
Sec-Fetch-Mode
cors
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36

Response headers

access-control-allow-headers
*
access-control-allow-methods
POST, OPTIONS
access-control-allow-origin
*
cf-cache-status
DYNAMIC
cf-ray
a36fcd84af6ee86b-FRA
date
Sun, 06 Sep 2026 19:15:30 GMT
server
cloudflare
strict-transport-security
max-age=31536000; includeSubDomains
vary
Origin
GET
H3
200
partnerpixels Show response
cm.g.doubleclick.net/ Frame E284
41 B
63 B
247ms
126ms
Document
text/html
142.251.13.157
Google LLC
General
Full URL
https://cm.g.doubleclick.net/partnerpixels?gpp=DBABLA~BVQqAAAAAAJY.QA&gpp_sid=7&url=https%3A%2F%2Fabc7.com%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.13.157 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
wt-in-f157.1e100.net
Software
HTTP server (unknown) /
Resource Hash
a09179dd962df38a01440ce2e4748c37bd832fe1ac2f65ad974490a89d63d129
Security Headers
Name Value
X-Xss-Protection 0

Request headers

Referer
https://abc7.com/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-encoding
gzip
content-length
48
content-type
text/html; charset=UTF-8
date
Sun, 06 Sep 2026 19:15:30 GMT
referrer-policy
origin
server
HTTP server (unknown)
x-xss-protection
0
GET
H3
200
sodar Show response
ep1.adtrafficquality.google/getconfig/
18 KB
13 KB
255ms
133ms
XHR
application/json
142.251.13.157
Google LLC
General
Full URL
https://ep1.adtrafficquality.google/getconfig/sodar?sv=200&tid=gpt&tv=m202609010101&st=env&sjk=8843972379179831
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.13.157 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
wt-in-f157.1e100.net
Software
cafe /
Resource Hash
ab3e54374fa7cd07830cf3d5a43902d85d787ec49cd512a08807ea48481e583d
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

timing-allow-origin
*
content-encoding
br
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
access-control-allow-origin
*
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
13544
date
Sun, 06 Sep 2026 19:15:30 GMT
x-xss-protection
0
content-type
application/json; charset=UTF-8
content-disposition
attachment; filename="f.txt"
server
cafe
GET
H2
200
sync.min.js Show response
tags.crwdcntrl.net/lt/c/16589/
45 KB
14 KB
414ms
144ms
Script
text/javascript
18.239.18.12
Amazon.com
General
Full URL
https://tags.crwdcntrl.net/lt/c/16589/sync.min.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
18.239.18.12 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-18-239-18-12.ams58.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
59f4e0057c651cb962d4637e70ff0d239f2b9c2cf4b31345d0145e03320b5b5a

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
cache-control
public, max-age=86400
content-encoding
gzip
etag
W/"16a2c198855d5eacecb864b94a4e05ff"
age
55895
via
1.1 9c7ba0aaf8652834e3f6b51b901da726.cloudfront.net (CloudFront)
alt-svc
h3=":443"; ma=86400
x-cache
Hit from cloudfront
x-amz-cf-id
IuC1nKpQJIdhL7XXpmCAPKu65qjvykD2DrNQ9SiLF3zkG13dsfrWRQ==
date
Sun, 06 Sep 2026 03:43:56 GMT
content-type
text/javascript
last-modified
Tue, 21 Apr 2026 21:53:16 GMT
server
AmazonS3
x-amz-cf-pop
AMS58-P6
x-amz-server-side-encryption
AES256
GET
H2
200
esp.js Show response
oa.openxcdn.net/
32 KB
10 KB
190ms
61ms
Script
text/javascript
34.102.146.192
Google LLC
General
Full URL
https://oa.openxcdn.net/esp.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.102.146.192 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
192.146.102.34.bc.googleusercontent.com
Software
UploadServer /
Resource Hash
6eb597e62d8b21162746327ebfef68ee2b73dc580d21c41ed789cce07ca6e8df

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
content-encoding
gzip
x-goog-hash
crc32c=CiZXGA==, md5=6ANS0cDK5cJvX1JTqLr+Bw==
etag
"e80352d1c0cae5c26f5f5253a8bafe07"
age
983706
x-goog-stored-content-encoding
gzip
expires
Thu, 26 Aug 2027 10:00:24 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
x-goog-stored-content-length
10025
date
Wed, 26 Aug 2026 10:00:24 GMT
last-modified
Mon, 27 Jul 2026 09:54:19 GMT
content-type
text/javascript
x-guploader-uploadid
AJjja9YFmVsMkjJtkcSOYSJnwZAk6k0zSYQuZGSbA4tq6wZdRhLjDsfFu2Wd2hx4xiXd8ctaY2SHA1Y
cache-control
no-transform
x-goog-storage-class
MULTI_REGIONAL
accept-ranges
bytes
x-goog-generation
1785146059317633
content-length
10025
server
UploadServer
GET
H2
200
novatiq_gam_integration.min.js Show response
cdn.fusion-platform.com/static/js/
4 KB
2 KB
371ms
119ms
Script
application/javascript
18.239.18.41
Amazon.com
General
Full URL
https://cdn.fusion-platform.com/static/js/novatiq_gam_integration.min.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
18.239.18.41 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-18-239-18-41.ams58.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
eebdef75652b741470090a179de485ded1abdb61500723854ed191731dbdf4fa

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
cache-control
public, max-age=86400, must-revalidate
content-encoding
gzip
x-amz-version-id
3sc4itUpz3RtVBZKmArbKWaVZ3mJ9T.0
etag
W/"96a305c59f820faf072fefef87f638b0"
age
64308
via
1.1 297dc74786919df7ba1867fc37f80bb6.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
JhCbF9qVwi8glBDV6OfI6uZG9NcS907eBHZKjhNTjv4NGzqh2nhk4g==
date
Sun, 06 Sep 2026 01:23:42 GMT
content-type
application/javascript
last-modified
Fri, 01 May 2026 15:51:10 GMT
server
AmazonS3
x-amz-cf-pop
AMS58-P6
x-amz-server-side-encryption
AES256
GET
H2
200
google-esp.js Show response
ads.pubmatic.com/AdServer/js/
9 KB
3 KB
352ms
118ms
Script
application/javascript
23.52.180.230
Akamai Technologies
General
Full URL
https://ads.pubmatic.com/AdServer/js/google-esp.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_256_GCM
Server
23.52.180.230 Frankfurt am Main, Germany, ASN16625 (AKAMAI-AS - Akamai Technologies, Inc., US),
Reverse DNS
a23-52-180-230.deploy.static.akamaitechnologies.com
Software
Apache /
Resource Hash
4fb83e9007857fd6beb489a96c88b4fb1370d68f7fb72f0cfc29abc059536e13

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=24661
content-encoding
gzip
expires
Mon, 07 Sep 2026 02:06:31 GMT
accept-ranges
bytes
p3p
CP="NOI DSP COR LAW CUR ADMo DEVo TAIo PSAo PSDo IVAo IVDo HISo OTPo OUR SAMo BUS UNI COM NAV INT DEM CNT STA PRE LOC", CP="NOI DSP COR LAW CUR ADMo DEVo TAIo PSAo PSDo IVAo IVDo HISo OTPo OUR SAMo BUS UNI COM NAV INT DEM CNT STA PRE LOC"
content-length
3130
date
Sun, 06 Sep 2026 19:15:30 GMT
last-modified
Mon, 03 Mar 2025 12:11:12 GMT
content-type
application/javascript
server
Apache
vary
Accept-Encoding
GET
H2
200
esp.js Show response
cdn.id5-sync.com/api/1.0/
118 KB
35 KB
349ms
123ms
Script
text/javascript
104.20.23.13
Cloudflare
General
Full URL
https://cdn.id5-sync.com/api/1.0/esp.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.20.23.13 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
a54e64c78ca21a728366ad30cf72c144662c7f59720a2766a570bbdb37874ea4
Security Headers
Name Value
Strict-Transport-Security max-age=15552000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-amz-id-2
C0Ldack2mf/mNRmlUSnj1V2eRiZCpxXTY1nPJGUIdrgaFQWtisIrHVE8IchWfINJSy8apIGWynTga77KRFvDvQzLMb2AnXMj
strict-transport-security
max-age=15552000; includeSubDomains; preload
cache-control
public, max-age=3600
content-encoding
br
cf-cache-status
HIT
etag
W/"de737ab89fa07f4a512e1c5b0834bd72"
age
2964
x-amz-request-id
2485JHZE7G08JXV8
cf-ray
a36fcd864deed26e-FRA
date
Sun, 06 Sep 2026 19:15:30 GMT
content-type
text/javascript;charset=utf-8
last-modified
Wed, 18 Mar 2026 12:22:23 GMT
server
cloudflare
x-amz-server-side-encryption
AES256
GET
H2
200
provider.js Show response
dmp.im-apps.net/secure-signal/
5 KB
2 KB
396ms
126ms
Script
text/javascript
2.16.241.207
AKAMAI-ASN1 Akama...
General
Full URL
https://dmp.im-apps.net/secure-signal/provider.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2.16.241.207 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a2-16-241-207.deploy.static.akamaitechnologies.com
Software
/
Resource Hash
34d4ea5d285d4bb5d24d9d353eabdb96fa8b2c9e899a73da01a8263b29da2ee7

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-amz-replication-status
COMPLETED
cache-control
public, max-age=3600
content-encoding
gzip
etag
"13e55ed530cc5a1e6b4194c4e54a23af"
x-amz-version-id
pePTzH2vYf7WqwMv3oOIH9WBgW3Td44F
expires
Sun, 06 Sep 2026 20:15:31 GMT
accept-ranges
bytes
content-length
2225
p3p
CP="NOI PSD OTR"
date
Sun, 06 Sep 2026 19:15:31 GMT
last-modified
Tue, 28 Jul 2026 04:04:19 GMT
content-type
text/javascript
vary
Accept-Encoding
x-amz-server-side-encryption
AES256
GET
H2
200
pubcid.min.js Show response
cdn.jsdelivr.net/gh/prebid/shared-id/pubcid.js/docs/
382 B
969 B
349ms
120ms
Script
application/javascript
104.17.207.5
Cloudflare
General
Full URL
https://cdn.jsdelivr.net/gh/prebid/shared-id/pubcid.js/docs/pubcid.min.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.17.207.5 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
6b9ae1fa0d1fc51ee0ad3feb565083bee200289c71bb346020f9b3d80cf73636
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

access-control-expose-headers
*
content-encoding
br
cf-cache-status
HIT
etag
W/"17e-goBKDsAq4SrgyL37A4bNh/aMb7I"
age
38187
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=bnMn4RAyvTzhI%2F6QmPNfEODeMhp3aEaxYDCvsDb7Oyfgz8jC%2FjH4pdSw6hA%2BrC7iibycjErq0NolvD4TXRMSnloYMU%2FFTGMdM3VGVzm9zAz4vRaY3ZhUI26KliXTUGaIs88%3D"}]}
x-content-type-options
nosniff
x-jsd-version-type
branch
alt-svc
h3=":443"; ma=86400
x-cache
HIT
date
Sun, 06 Sep 2026 19:15:31 GMT
content-type
application/javascript; charset=utf-8
x-served-by
cache-fra-etou8220025-FRA
vary
Accept-Encoding
strict-transport-security
max-age=31536000; includeSubDomains; preload
cache-control
public, max-age=604800, s-maxage=43200
timing-allow-origin
*
nel
{"report_to":"cf-nel","success_fraction":0.01,"max_age":604800}
cross-origin-resource-policy
cross-origin
cf-ray
a36fcd86fc69a6a2-FRA
accept-ranges
bytes
access-control-allow-origin
*
content-length
237
server
cloudflare
x-jsd-version
HEAD
GET
H2
200
connectId-gpt.js Show response
connectid.analytics.yahoo.com/
9 KB
9 KB
437ms
136ms
Script
application/javascript
18.66.102.31
Amazon.com
General
Full URL
https://connectid.analytics.yahoo.com/connectId-gpt.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
18.66.102.31 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-18-66-102-31.fra56.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
56351c084d8d56437d41f1e58b7eb184b563871e88bab60f6b15486c39f13996
Security Headers
Name Value
Content-Security-Policy default-src 'self'

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

etag
"faa388a163b1b6d0377ee77a861591e5"
age
906
x-cache
Hit from cloudfront
x-amz-cf-id
cosXs1vmWyN0YwWTSjh8M5RlZh-nJN9oc8rQ4MwOaRY7LsTLVwUZOg==
date
Sun, 06 Sep 2026 19:00:26 GMT
content-type
application/javascript
last-modified
Mon, 22 Apr 2024 18:18:45 GMT
x-amz-expiration
expiry-date="Mon, 23 Apr 2029 00:00:00 GMT", rule-id="webapp-standard-lifecycle"
content-security-policy
default-src 'self'
cache-control
max-age=3600
via
1.1 03ffca0f67e3596b9a0c92342fe91598.cloudfront.net (CloudFront)
accept-ranges
bytes
content-length
8729
x-amz-cf-pop
FRA56-P2
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H3
200
myGaruStandalone.js Show response
cdn.mgaru.dev/static/
3 KB
2 KB
259ms
129ms
Script
application/javascript
172.67.205.57
Cloudflare
General
Full URL
https://cdn.mgaru.dev/static/myGaruStandalone.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.67.205.57 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
dcb1ae2a48400b7963d5b7da7643c2907eaff88863931a3fdcde9e64538aa5e0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
cf-cache-status
HIT
etag
"6a7495f0-aad"
age
159
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=q%2BuOdKiWie28gzESEphWvzorgg%2BpRM%2FF9iqcVg0T5w7E5qSTEOEjXLZtTSZ63in%2Bt0dbmHzWArwoOwXP5fi2Hb6V0O223VkRTXSnqT98GYoDWNF5FJioYLZ0PKoC9cNn"}]}
expires
Sun, 06 Sep 2026 19:27:51 GMT
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Sun, 06 Sep 2026 19:15:30 GMT
content-type
application/javascript
last-modified
Thu, 06 Aug 2026 14:10:56 GMT
vary
accept-encoding
priority
u=3,i=?0
cache-control
max-age=14400
timing-allow-origin
*
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
cf-ray
a36fcd867a453c32-AMS
server
cloudflare
GET
H2
200
encrypted-tag-g.js Show response
invstatic101.creativecdn.com/encrypted-signals/
3 KB
3 KB
445ms
311ms
Script
text/javascript
34.96.70.87
Google LLC
General
Full URL
https://invstatic101.creativecdn.com/encrypted-signals/encrypted-tag-g.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.96.70.87 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
87.70.96.34.bc.googleusercontent.com
Software
Google Frontend /
Resource Hash
2e5f5cb912c0619933ea6c3ad8ac1466a005f792e3338d96a8432d144c63520f

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

etag
861bdaf24bda5c0db45c6ebe1c94a9eb
via
1.1 google
alt-svc
h3=":443"; ma=2592000
content-length
2729
date
Sun, 06 Sep 2026 19:15:31 GMT
content-type
text/javascript; charset=utf-8
last-modified
Wed, 05 Feb 2025 14:45:21 GMT
server
Google Frontend
x-cloud-trace-context
5e7e749475bf69e93ee9a6e0f01cee9f
GET
H3
200
ads Show response
securepubads.g.doubleclick.net/gampad/
41 KB
8 KB
461ms
460ms
Fetch
text/plain
142.250.154.154
Google LLC
General
Full URL
https://securepubads.g.doubleclick.net/gampad/ads?pvsid=8843972379179831&correlator=1652442865289150&hxva=1&scor=2092584856347766&eid=122880805%2C122880806&output=ldjh&gdfp_req=1&vrg=202609010101&ptt=17&impl=fifs&gpp=DBABLA~BVQqAAAAAAJY.QA&gpp_sid=7&iu_parts=21783347309%2Ckabc%2Cabc7.com%2Cweb%2Cdisasters-accidents&enc_prev_ius=%2F0%2F1%2F2%2F3%2F4%2C%2F0%2F1%2F2%2F3%2F4%2C%2F0%2F1%2F2%2F3%2F4&prev_iu_szs=970x250%7C970x66%7C728x90%2C300x250%7C300x600%2C1x1&ifi=1&didk=2819283520~2002766480~1051142217&dids=ad-slot-fitt-article-top-banne~ad-slot-fitt-article-right-rai~ad-slot-interstitial-881981&adfs=1953764155~2843284357~3780849393&sfv=1-0-45&eri=1&sc=1&cookie_enabled=1&abxe=1&dt=1788722130475&lmt=1788722132&adxs=315%2C1074%2C0&adys=72%2C1460%2C7435&biw=1600&bih=1200&scr_x=0&scr_y=0&btvi=0%7C1%7C2&ucis=1%7C2%7C3&oid=2&u_his=1&u_h=1200&u_w=1600&u_ah=1200&u_aw=1600&u_cd=24&u_sd=1&u_tz=180&dmc=32&bc=31&nvt=1&uach=WyJMaW51eCIsIiIsIng4NiIsIiIsIjE1Mi4wLjc5NzcuODIiLG51bGwsMCxudWxsLCI2NCIsW1siQ2hyb21pdW0iLCIxNTIuMC43OTc3LjY0Il0sWyJHb29nbGUgQ2hyb21lIiwiMTUyLjAuNzk3Ny42NCJdLFsiTm90P0FfQnJhbmQiLCIyNC4wLjAuMCJdXSwwXQ..&url=https%3A%2F%2Fabc7.com%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F&vis=1&psz=1600x0%7C400x0%7C1600x0&msz=1600x0%7C400x0%7C1600x0&fws=512%2C0%2C0&ohw=0%2C0%2C0&dlt=1788722126353&idt=4027&prev_scp=pos%3Dfitt-article-top-banner%7Cpos%3Dfitt-article-right-rail%7Cpos%3Dinterstitial&cust_params=aff%3Dkabc%26chan%3Dkabc%26lang%3Den%26pgn%3D19779712%26pgtyp%3Darticle%26objid%3D19779712%26tag%3Dearthquake%252Cusgs%252Contario%252Csan-bernardino-county%26hip%3Dip_error%26d_us_privacy%3D1YYY%26inskin_yes%3Dyes%26prof%3Dl&adks=477828860%2C656094119%2C3376130863&frm=20&eoidce=1&pgls=CAk.
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.250.154.154 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bt-in-f154.1e100.net
Software
cafe /
Resource Hash
02bd8ecfd3623de355101443ed91980ac437882d55980ce3c2b61da4a2a7b82c
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
dcb
google-lineitem-id
-1,-2,-2
x-content-type-options
nosniff
google-mediationtag-id
-2
google-mediationgroup-id
-2,-2
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
date
Sun, 06 Sep 2026 19:15:30 GMT
content-type
text/plain; charset=UTF-8
google-creative-id
-1,-2,-2
cache-control
no-cache, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
access-control-allow-origin
https://abc7.com
content-length
7872
x-xss-protection
0
server
cafe
GET
H2
200
container.html Show response
0c94aa5156cf0935a827c3b9863ae691.safeframe.googlesyndication.com/safeframe/1-0-45/html/ Frame CD6A
7 KB
3 KB
377ms
126ms
Document
text/html
142.251.110.132
Google LLC
General
Full URL
https://0c94aa5156cf0935a827c3b9863ae691.safeframe.googlesyndication.com/safeframe/1-0-45/html/container.html
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.110.132 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f132.1e100.net
Software
sffe /
Resource Hash
f1a68bf826c55985468304f4284a09cb8a68e82503d764166e611a7c58a85a4b
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://abc7.com/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

accept-ranges
bytes
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cache-control
private, max-age=300
content-encoding
br
content-length
3121
content-type
text/html
cross-origin-opener-policy-report-only
same-origin; report-to="ads-gpt-scs"
cross-origin-resource-policy
cross-origin
date
Sun, 06 Sep 2026 19:15:30 GMT
expires
Sun, 06 Sep 2026 19:15:30 GMT
last-modified
Thu, 08 May 2025 23:15:48 GMT
report-to
{"group":"ads-gpt-scs","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/ads-gpt-scs"}]}
server
sffe
timing-allow-origin
*
vary
Accept-Encoding
x-content-type-options
nosniff
x-xss-protection
0
GET
H2
204
b2
sb.scorecardresearch.com/
Redirect Chain
  • https://sb.scorecardresearch.com/b?c1=2&c2=3000032&cs_fpcu=b49559bb63a0492fa9326a9ab40a120b&cs_it=b1&cv=4.13.1%2B2508250908&ns__t=1788722130539&ns_c=UTF-8&cs_cfg=1101110&cs_ucc=1&cs_cmp_id=28&gpp_s...
  • https://sb.scorecardresearch.com/b2?c1=2&c2=3000032&cs_fpcu=b49559bb63a0492fa9326a9ab40a120b&cs_it=b1&cv=4.13.1%2B2508250908&ns__t=1788722130539&ns_c=UTF-8&cs_cfg=1101110&cs_ucc=1&cs_cmp_id=28&gpp_...
0
225 B
120ms
119ms
Image
text/plain
18.244.18.27
Amazon.com
General
Full URL
https://sb.scorecardresearch.com/b2?c1=2&c2=3000032&cs_fpcu=b49559bb63a0492fa9326a9ab40a120b&cs_it=b1&cv=4.13.1%2B2508250908&ns__t=1788722130539&ns_c=UTF-8&cs_cfg=1101110&cs_ucc=1&cs_cmp_id=28&gpp_ssv=1&gpp_gpc=0&gpp_oos=222&gpp_oon=1X11100&gpp_sdp=0000000000000000&gpp_pdc=2&gpp_cdc=000&gpp_mct=1&gpp_mom=1&gpp_msm=2&cs_cmp_ie=10&cs_cmp_rt=0&cs_cmp_av=1.1&gpp_sid=7&gpp_smv=1.1&c7=https%3A%2F%2Fabc7.com%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F&c8=3.4-magnitude%20earthquake%20hits%20Ontario%2C%20shaking%20felt%20across%20San%20Bernardino%20County%2C%20USGS%20says%20-%20ABC7%20Los%20Angeles&c9=
Protocol
H2
Server
18.244.18.27 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-18-244-18-27.fra56.r.cloudfront.net
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
Referer
https://abc7.com/

Response headers

via
1.1 d025091c574ce1bcf1fefea59ac34f2c.cloudfront.net (CloudFront)
x-cache
Miss from cloudfront
x-amz-cf-id
I4FsaBNr1wxrZWTsE-GrrglR7VRZdKSpQVCdSkN6wIEqJILMBcxcoA==
date
Sun, 06 Sep 2026 19:15:30 GMT
accept-ch
UA, Platform, Arch, Model, Mobile
x-amz-cf-pop
FRA56-P11

Redirect headers

location
/b2?c1=2&c2=3000032&cs_fpcu=b49559bb63a0492fa9326a9ab40a120b&cs_it=b1&cv=4.13.1%2B2508250908&ns__t=1788722130539&ns_c=UTF-8&cs_cfg=1101110&cs_ucc=1&cs_cmp_id=28&gpp_ssv=1&gpp_gpc=0&gpp_oos=222&gpp_oon=1X11100&gpp_sdp=0000000000000000&gpp_pdc=2&gpp_cdc=000&gpp_mct=1&gpp_mom=1&gpp_msm=2&cs_cmp_ie=10&cs_cmp_rt=0&cs_cmp_av=1.1&gpp_sid=7&gpp_smv=1.1&c7=https%3A%2F%2Fabc7.com%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F&c8=3.4-magnitude%20earthquake%20hits%20Ontario%2C%20shaking%20felt%20across%20San%20Bernardino%20County%2C%20USGS%20says%20-%20ABC7%20Los%20Angeles&c9=
accept-ch
UA, Platform, Arch, Model, Mobile
via
1.1 d025091c574ce1bcf1fefea59ac34f2c.cloudfront.net (CloudFront)
x-cache
Miss from cloudfront
content-length
0
x-amz-cf-id
cvB6vYQs5Q0g1SgDhpsYa_hzHyZcIOCbyDuY7u-swbcYG1m8T7Njkw==
date
Sun, 06 Sep 2026 19:15:30 GMT
x-amz-cf-pop
FRA56-P11
GET
H2
200
log Show response
log.go.com/
1 B
342 B
191ms
189ms
Fetch
application/octet-stream
15.197.135.246
Amazon.com
General
Full URL
https://log.go.com/log?appid=IDENTITY-SDK-V5&sdk_version=web+5.1.30-qa.0&conversation_id=7e1df8d8-bd78-4f23-9863-277becde8879&language=en-US&sdk_install_id=2627c924-96e2-4c09-a5ce-389cc2d6003e&detected_country=US&event_start_time=1788722130547&action_name=event%3Ainit&info=payloadincluded%28false%29&client_id=DATG-OTV.KABC.WEB-PROD&timestamp=1788722130547&swid=76d9eb61-6562-4b6d-a09d-8ea2b1296ac4
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
15.197.135.246 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
a7b7d02f3736e735c.awsglobalaccelerator.com
Software
/
Resource Hash
36a9e7f1c95b82ffb99743e0c5c4ce95d83c9a430aac59f84ef3cbfab6145068

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
900
cache-control
no-cache
pragma
no-cache
access-control-allow-credentials
true
access-control-allow-methods
GET, POST, OPTIONS
allow
GET, OPTIONS
expires
0
access-control-allow-origin
https://abc7.com
date
Sun, 06 Sep 2026 19:15:30 GMT
content-type
application/octet-stream
vary
Origin
GET
H2
200
log Show response
log.go.com/
1 B
342 B
238ms
237ms
Fetch
application/octet-stream
15.197.135.246
Amazon.com
General
Full URL
https://log.go.com/log?appid=IDENTITY-SDK-V5&sdk_version=web+5.1.30-qa.0&conversation_id=cfcc3c3d-8f5c-4ec9-9a05-05993e4ddbb6&language=en-US&sdk_install_id=2627c924-96e2-4c09-a5ce-389cc2d6003e&detected_country=US&swid=76d9eb61-6562-4b6d-a09d-8ea2b1296ac4&event_start_time=1788722130552&info=detectedcountry%28IL%29%2Ccampaignid%28Breaking+News%29&level=40&error_category=FAILURE_BY_DESIGN&error_codes=INVALID_LOCATION&action_name=api%3Aget%3Ainlinenewsletters&process_time=0&client_id=DATG-OTV.KABC.WEB-PROD&timestamp=1788722130552
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
15.197.135.246 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
a7b7d02f3736e735c.awsglobalaccelerator.com
Software
/
Resource Hash
36a9e7f1c95b82ffb99743e0c5c4ce95d83c9a430aac59f84ef3cbfab6145068

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
900
cache-control
no-cache
pragma
no-cache
access-control-allow-credentials
true
access-control-allow-methods
GET, POST, OPTIONS
allow
GET, OPTIONS
expires
0
access-control-allow-origin
https://abc7.com
date
Sun, 06 Sep 2026 19:15:30 GMT
content-type
application/octet-stream
vary
Origin
HEAD
H2
200
css2
fonts.googleapis.com/
0
0
361ms
122ms
Fetch
text/css
142.251.14.95
Google LLC
General
Full URL
https://fonts.googleapis.com/css2?family=Montserrat&text=a
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
142.251.14.95 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f95.1e100.net
Software
ESF /
Resource Hash
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-content-type-options
nosniff
expires
Sun, 06 Sep 2026 19:15:30 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sun, 06 Sep 2026 19:15:30 GMT
content-type
text/css; charset=utf-8
vary
Sec-Fetch-Dest, Sec-Fetch-Mode, Sec-Fetch-Site
last-modified
Sun, 06 Sep 2026 18:04:02 GMT
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=31536000
link
<https://fonts.gstatic.com>; rel=preconnect; crossorigin
cache-control
private, max-age=86400, stale-while-revalidate=604800
timing-allow-origin
*
cross-origin-opener-policy
same-origin-allow-popups
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
content-length
0
x-xss-protection
0
server
ESF
GET
H2
200
kabc-background-mobile.webp
cdn.registerdisney.go.com/v4/asset/bundler/KABC/v4/images/v1/ Frame 4730
20 KB
21 KB
1720ms
1409ms
Image
image/webp
23.56.204.67
Akamai Technologies
General
Full URL
https://cdn.registerdisney.go.com/v4/asset/bundler/KABC/v4/images/v1/kabc-background-mobile.webp
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
23.56.204.67 Frankfurt am Main, Germany, ASN16625 (AKAMAI-AS - Akamai Technologies, Inc., US),
Reverse DNS
a23-56-204-67.deploy.static.akamaitechnologies.com
Software
/
Resource Hash
355b91779320942fe781008e2bfcbde6291ada879e5e2671ac0124854815ad97

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

access-control-allow-headers
Cache-Control,Content-Type,Expires,If-None-Match,Pragma
cache-control
max-age=900, must-revalidate, public
access-control-allow-origin
*
content-length
20840
date
Sun, 06 Sep 2026 19:15:32 GMT
access-control-allow-methods
GET,HEAD,OPTIONS
GET
H2
200
kabc-logo.svg
cdn.registerdisney.go.com/v4/asset/bundler/KABC/v4/images/v1/ Frame 4730
5 KB
2 KB
744ms
434ms
Image
image/svg+xml
23.56.204.67
Akamai Technologies
General
Full URL
https://cdn.registerdisney.go.com/v4/asset/bundler/KABC/v4/images/v1/kabc-logo.svg
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
23.56.204.67 Frankfurt am Main, Germany, ASN16625 (AKAMAI-AS - Akamai Technologies, Inc., US),
Reverse DNS
a23-56-204-67.deploy.static.akamaitechnologies.com
Software
/
Resource Hash
80ddf5dd9f500cac2109e28a4e890188f7559f5920db1e609db9ec7c49fe2600

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=900, must-revalidate, public
content-encoding
gzip
etag
"129b-w6AgKkUJd5tr1SU8t+fXa8ZffHU"
access-control-allow-methods
GET,HEAD,OPTIONS
access-control-allow-origin
*
content-length
2108
date
Sun, 06 Sep 2026 19:15:31 GMT
content-type
image/svg+xml
vary
Accept-Encoding
access-control-allow-headers
Cache-Control,Content-Type,Expires,If-None-Match,Pragma
GET
H2
200
Utility.00095afa.svg
login.disney.com/_next/static/media/ Frame 4730
1 KB
1002 B
198ms
198ms
Image
image/svg+xml
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/media/Utility.00095afa.svg
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/css/d8901c280c38085c.css?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
1c60f6223cedb212ae2c80a936f3d6f5092a95a59659cb8c79c96a7492e5c109

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/_next/static/css/d8901c280c38085c.css?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
e9d435c836dacdf9e8cab78b861d711c
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"4ab-1a01fc3c5d8"
age
1473332
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
hjo6Gh19JIrz1FtkBcVO_jSB-12F2thYxNB3fOftU88yqjF4p9FdIQ==
date
Thu, 20 Aug 2026 17:59:58 GMT
content-type
image/svg+xml
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
DATA
200
OK
truncated
/ Frame 4730
252 B
0
Image
image/svg+xml

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
d6039d3cd0846558a77f2259c6c671f3d395ac9dd99836ab3d2a8f901029e5d1

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/svg+xml
GET
H3
200
o-0bIpQlx3QUlC5A4PNB6Ryti20_6n1iPHjc5a7du3mhPy0.woff2
fonts.gstatic.com/s/notosans/v36/ Frame 4730
38 KB
38 KB
248ms
124ms
Font
font/woff2
142.251.14.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/notosans/v36/o-0bIpQlx3QUlC5A4PNB6Ryti20_6n1iPHjc5a7du3mhPy0.woff2
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/css/de38fa60eef746e1.css?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.14.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f94.1e100.net
Software
sffe /
Resource Hash
e357b02137741b5640a01eb60531cc5b9f1ad6af0797abd26d34249073fb11b2
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://login.disney.com
sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

age
184829
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Sat, 04 Sep 2027 15:55:01 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 04 Sep 2026 15:55:01 GMT
last-modified
Wed, 14 Feb 2024 22:44:14 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
39372
x-xss-protection
0
server
sffe
GET
H3
200
o-0bIpQlx3QUlC5A4PNB6Ryti20_6n1iPHjc5ardu3mhPy1Fig.woff2
fonts.gstatic.com/s/notosans/v36/ Frame 4730
21 KB
21 KB
291ms
168ms
Font
font/woff2
142.251.14.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/notosans/v36/o-0bIpQlx3QUlC5A4PNB6Ryti20_6n1iPHjc5ardu3mhPy1Fig.woff2
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/css/de38fa60eef746e1.css?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.14.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f94.1e100.net
Software
sffe /
Resource Hash
fa57a0c44b9b57a2f736e923b0a400fba8ba99035b691a71c1087b15f1eedb9e
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://login.disney.com
sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

age
169539
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Sat, 04 Sep 2027 20:09:51 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 04 Sep 2026 20:09:51 GMT
last-modified
Wed, 14 Feb 2024 22:40:06 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
21304
x-xss-protection
0
server
sffe
GET
H3
200
o-0bIpQlx3QUlC5A4PNB6Ryti20_6n1iPHjc5aDdu3mhPy1Fig.woff2
fonts.gstatic.com/s/notosans/v36/ Frame 4730
137 KB
137 KB
332ms
209ms
Font
font/woff2
142.251.14.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/notosans/v36/o-0bIpQlx3QUlC5A4PNB6Ryti20_6n1iPHjc5aDdu3mhPy1Fig.woff2
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/css/de38fa60eef746e1.css?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.14.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f94.1e100.net
Software
sffe /
Resource Hash
8bd21bce2fceef2e4aa489ae8e3dab11d3997fdea5a4d63163356f0abc96e547
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://login.disney.com
sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

age
169393
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Sat, 04 Sep 2027 20:12:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 04 Sep 2026 20:12:17 GMT
last-modified
Wed, 14 Feb 2024 22:29:09 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
140408
x-xss-protection
0
server
sffe
GET
H3
200
o-0bIpQlx3QUlC5A4PNB6Ryti20_6n1iPHjc5a3du3mhPy1Fig.woff2
fonts.gstatic.com/s/notosans/v36/ Frame 4730
23 KB
23 KB
377ms
254ms
Font
font/woff2
142.251.14.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/notosans/v36/o-0bIpQlx3QUlC5A4PNB6Ryti20_6n1iPHjc5a3du3mhPy1Fig.woff2
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/css/de38fa60eef746e1.css?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.14.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f94.1e100.net
Software
sffe /
Resource Hash
80303d7fba1a41c684f1e6d5dcb015bf6e087dfbe45f8d9d8f38972e84adc174
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://login.disney.com
sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

age
173308
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Sat, 04 Sep 2027 19:07:02 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 04 Sep 2026 19:07:02 GMT
last-modified
Wed, 14 Feb 2024 22:40:12 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
23564
x-xss-protection
0
server
sffe
GET
H3
200
iJWQBXeUZi_OHPqn4wq6hQ2_hbJ1xyN9wd43SofNWcdfKI2hX2g.woff2
fonts.gstatic.com/s/notosansthai/v29/ Frame 4730
26 KB
26 KB
419ms
296ms
Font
font/woff2
142.251.14.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/notosansthai/v29/iJWQBXeUZi_OHPqn4wq6hQ2_hbJ1xyN9wd43SofNWcdfKI2hX2g.woff2
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/css/de38fa60eef746e1.css?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.14.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f94.1e100.net
Software
sffe /
Resource Hash
1f5a173641bbcb3ca4fb0a986858b6b07f8cd5dd2ed61236b40548c7a3c7292f
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://login.disney.com
sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

age
169883
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Sat, 04 Sep 2027 20:04:07 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 04 Sep 2026 20:04:07 GMT
last-modified
Thu, 04 Sep 2025 17:21:38 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
26924
x-xss-protection
0
server
sffe
GET
H3
200
o-0bIpQlx3QUlC5A4PNB6Ryti20_6n1iPHjc5aHdu3mhPy1Fig.woff2
fonts.gstatic.com/s/notosans/v36/ Frame 4730
16 KB
16 KB
241ms
118ms
Font
font/woff2
142.251.14.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/notosans/v36/o-0bIpQlx3QUlC5A4PNB6Ryti20_6n1iPHjc5aHdu3mhPy1Fig.woff2
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/css/de38fa60eef746e1.css?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.14.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f94.1e100.net
Software
sffe /
Resource Hash
1ae2d576bcdce140d46ee230157ec7cc1d2b3d3aee20d33a99ff72e63180b5c4
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://login.disney.com
sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

age
171601
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Sat, 04 Sep 2027 19:35:29 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 04 Sep 2026 19:35:29 GMT
last-modified
Wed, 14 Feb 2024 22:42:29 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
15892
x-xss-protection
0
server
sffe
OPTIONS
H2
204
graphql
login.disney.com/api/ Frame
0
0
123ms
123ms
Preflight
3.161.82.34
Amazon.com
General
Full URL
https://login.disney.com/api/graphql
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.34 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-34.fra56.r.cloudfront.net
Software
/
Resource Hash

Request headers

Accept
*/*
Access-Control-Request-Headers
content-type,x-disney-identity-client-id,x-disney-identity-language-preference
Access-Control-Request-Method
POST
Origin
https://abc7.com
Sec-Fetch-Mode
cors
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36

Response headers

access-control-allow-credentials
true
access-control-allow-headers
content-type,x-disney-identity-client-id,x-disney-identity-language-preference
access-control-allow-methods
GET, POST, PUT, PATCH, DELETE, OPTIONS
access-control-allow-origin
https://abc7.com
access-control-expose-headers
x-request-id, x-bamtech-region, date
access-control-max-age
600
age
1280
cache-control
public, max-age=3600
date
Sun, 06 Sep 2026 18:54:10 GMT
vary
origin,access-control-request-headers
via
1.1 9c8021538470ab47dffa34921d0b4aca.cloudfront.net (CloudFront)
x-amz-cf-id
9wQr1TeJRrmZU6TG75LAHD5I8TNouPmF8O42xFqS0y2FC_dpuBA-Eg==
x-amz-cf-pop
FRA56-P10
x-bamtech-region
eu-central-1
x-cache
Hit from cloudfront
x-request-id
edf04e2dd9d8c3d138e4bbb593b10917
POST
H2
200
graphql Show response
login.disney.com/api/
2 KB
2 KB
161ms
160ms
Fetch
application/json
3.161.82.34
Amazon.com
General
Full URL
https://login.disney.com/api/graphql
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.34 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-34.fra56.r.cloudfront.net
Software
/
Resource Hash
ffca8feeed03b2fd66a3f25ca52e0cb865048fc7f1a73ea0d1c3cee12378ee7b

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
x-disney-identity-language-preference
en-US
x-disney-identity-client-id
DATG-OTV.KABC.WEB
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
content-type
application/json

Response headers

access-control-max-age
600
x-request-id
04a305cdc7c32f99fe998f90da2896b1
access-control-expose-headers
x-request-id, x-bamtech-region, date
content-encoding
gzip
access-control-allow-methods
GET, POST, PUT, PATCH, DELETE, OPTIONS
x-cache
Miss from cloudfront
x-amz-cf-id
_jm9Z7sw5SAI-jq07R1EUwDTHgdkHM4dikdPA_othjzad0ORTHNAOA==
date
Sun, 06 Sep 2026 19:15:30 GMT
content-type
application/json
vary
origin, access-control-request-headers
cache-control
no-store
apollo-trace-id
c81b14e2b4f918472fab89061e40fed8
access-control-allow-credentials
true
x-bamtech-region
eu-central-1
via
1.1 9c8021538470ab47dffa34921d0b4aca.cloudfront.net (CloudFront)
access-control-allow-origin
https://abc7.com
x-amz-cf-pop
FRA56-P10
GET
H/1.1
200
OK
score.min.js Show response
js.ad-score.com/
580 KB
181 KB
370ms
134ms
Script
application/javascript
18.245.60.26
Amazon.com
General
Full URL
https://js.ad-score.com/score.min.js?pid=1000075
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_128_GCM
Server
18.245.60.26 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-18-245-60-26.fra60.r.cloudfront.net
Software
/
Resource Hash
bd38e3672ae4700954e2db246eea1be482fd4c25ad762235977ea32c4c6fc52d

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

Content-Encoding
br
Age
18296
Access-Control-Allow-Methods
GET
Expires
Mon, 07 Sep 2026 14:10:35 GMT
X-Cache
Hit from cloudfront
X-Amz-Cf-Id
h2jhRiHZMAO1vYgKEIJ1MgSSRKW8pcA1Fn5Oc7r3ez6t2WLXd4zWHQ==
Date
Sun, 06 Sep 2026 14:10:35 GMT
Content-Type
application/javascript
Last-Modified
Sun, 06 Sep 2026 14:10:35 GMT
Vary
Accept-Encoding
Access-Control-Allow-Headers
Cache-Control
Transfer-Encoding
chunked
Cache-Control
public, max-age=86400
Connection
keep-alive
Access-Control-Allow-Credentials
true
Via
1.1 69a82a9746d3a7343dca651e0829f000.cloudfront.net (CloudFront)
Access-Control-Allow-Origin
*
X-Amz-Cf-Pop
FRA60-P5
GET
DATA
200
OK
truncated
/
73 B
73 B
Image
image/svg

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
38814c5240d913c5270db8b8c3eae9f192489b2d2752b63c30562c4287f70015

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/svg
GET
H2
204
/ Show response
cds.taboola.com/
0
82 B
598ms
183ms
XHR
text/plain
141.226.224.32
TABOOLA-AS Tabool...
General
Full URL
https://cds.taboola.com/?uid=419acdb7-b09e-4b32-b034-56c31d5fd705-tuct11974151&ptf=TGludXg=&ufv=MTUyLjAuNzk3Ny44Mg==&bnd=Q2hyb21pdW0=&bndv=MTUy&bnd=R29vZ2xlIENocm9tZQ==&bndv=MTUy&bnd=Tm90P0FfQnJhbmQ=&bndv=MjQ=&mbl=ZmFsc2U=&dc=il
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.2, ECDHE_ECDSA, AES_128_GCM
Server
141.226.224.32 Newark, United States, ASN200478 (TABOOLA-AS Taboola.com ltd, IL),
Reverse DNS
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

access-control-allow-origin
*
cache-control
no-store
date
Sun, 06 Sep 2026 19:15:31 GMT
server
nginx
POST
H2
204
debug
il-trc-events.taboola.com/abcotvweb-abc7la/log/2/
0
123 B
114ms
112ms
Ping
text/plain
185.106.33.48
TABOOLA-AS Tabool...
General
Full URL
https://il-trc-events.taboola.com/abcotvweb-abc7la/log/2/debug?type=warn&msg=Placements%20With%20no%20Content%3A%20Below%20Article%20Thumbnails%20%7C%20Lazy%20Injected%201&lt=default&tvi48=32980&tvi50=32540&tim=22%3A15%3A30.618&id=25712&cv=20260906-3-RELEASE&llvl=2
Requested by
Host: cdn.taboola.com
URL: https://cdn.taboola.com/libtrc/abcotvweb-network/loader.js
Protocol
H2
Security
TLS 1.2, ECDHE_ECDSA, AES_128_GCM
Server
185.106.33.48 , Israel, ASN200478 (TABOOLA-AS Taboola.com ltd, IL),
Reverse DNS
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
Content-Type
application/x-www-form-urlencoded
sec-ch-ua-mobile
?0

Response headers

access-control-allow-origin
https://abc7.com
x-fastly-to-nlb-rtt
55520
date
Sun, 06 Sep 2026 19:15:30 GMT
server
nginx
access-control-allow-credentials
true
POST
H2
204
debug
il-trc-events.taboola.com/abcotvweb-abc7la/log/2/
0
123 B
114ms
114ms
Ping
text/plain
185.106.33.48
TABOOLA-AS Tabool...
General
Full URL
https://il-trc-events.taboola.com/abcotvweb-abc7la/log/2/debug?type=warn&msg=Placements%20With%20no%20Content%3A%20Below%20Article%20Thumbnails%20%7C%20Lazy%20Injected%201&lt=default&tvi48=32980&tvi50=32540&tim=22%3A15%3A30.620&id=24697&cv=20260906-3-RELEASE&llvl=2
Requested by
Host: cdn.taboola.com
URL: https://cdn.taboola.com/libtrc/abcotvweb-network/loader.js
Protocol
H2
Security
TLS 1.2, ECDHE_ECDSA, AES_128_GCM
Server
185.106.33.48 , Israel, ASN200478 (TABOOLA-AS Taboola.com ltd, IL),
Reverse DNS
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
Content-Type
application/x-www-form-urlencoded
sec-ch-ua-mobile
?0

Response headers

access-control-allow-origin
https://abc7.com
x-fastly-to-nlb-rtt
55520
date
Sun, 06 Sep 2026 19:15:30 GMT
server
nginx
access-control-allow-credentials
true
GET

19779720_090226-kabc-ontario-quake-tn.jpg
cdn.abcotvs.com/dip/images/
0
0


GET
DATA
200
OK
truncated
/
42 B
0
Image
image/gif

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/gif
GET
H2
200
4864-32079439.js Show response
assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/
9 KB
3 KB
108ms
107ms
Script
application/javascript
13.32.121.29
Amazon.com
General
Full URL
https://assets-cdn.abcotvs.net/abcotv/77b7d8b8a917-release-09-02-2026.14/client/abcotv/4864-32079439.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.29 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-29.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
4b311193401567ec21f742d088da5bb2b074d619f4cc405c6ec857ae02e0a4d1

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
br
etag
W/"45a2eb81ad60d367db4468e3927e9f3b"
age
358131
via
1.1 c2856877bfae (Varnish/7.5), 1.1 06a27d66e25d02ebcfb014b9d194016a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
x-amz-cf-id
wf9AyrDFv0nKf9W9BkCkJFIbwIE_xB1HLlXFBXvgfYkSoFtS2Wsj0A==
date
Wed, 02 Sep 2026 15:46:39 GMT
content-type
application/javascript
last-modified
Wed, 02 Sep 2026 01:36:34 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
vary
Accept-Encoding
GET
H2
200
abc_news Show response
pcs.bamgrid.com/v1/
1 KB
1 KB
125ms
124ms
XHR
application/json
13.226.244.19
Amazon.com
General
Full URL
https://pcs.bamgrid.com/v1/abc_news?brand=google&platform=chrome&os=linux&namespaces=hive-dmp,ads,pqm
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.226.244.19 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-226-244-19.fra56.r.cloudfront.net
Software
/
Resource Hash
3005cd8a92a5c20d9a596716643de6e8f91d9b5360bf2964ffaa13b5bdf6607c

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
600
x-request-id
edb66fa89b13ccf4d3969a31b0b71bd1
access-control-expose-headers
x-request-id, x-bamtech-region, date
content-encoding
gzip
age
47405
access-control-allow-methods
GET, POST, PUT, PATCH, DELETE, OPTIONS
x-bypass-cache
false
x-cache
Hit from cloudfront
x-amz-cf-id
cRnNVuKG68HylnLp5cTxCxRg9ChLonHiQTgjrjxcyGKdxWVfijGnMQ==
date
Sun, 06 Sep 2026 06:05:25 GMT
content-type
application/json
vary
origin
cache-control
s-maxage=31536000
access-control-allow-credentials
true
x-bamtech-region
eu-central-1
via
1.1 ede4657ca75ee1968129a6a3c26144b0.cloudfront.net (CloudFront)
access-control-allow-origin
https://abc7.com
x-amz-cf-pop
FRA56-P14
GET
H2
200
abc_news Show response
pcs.bamgrid.com/v1/
1 KB
1 KB
253ms
128ms
XHR
application/json
13.226.244.19
Amazon.com
General
Full URL
https://pcs.bamgrid.com/v1/abc_news?brand=google&platform=chrome&os=linux&namespaces=hive-dmp,ads,pqm
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.226.244.19 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-226-244-19.fra56.r.cloudfront.net
Software
/
Resource Hash
3005cd8a92a5c20d9a596716643de6e8f91d9b5360bf2964ffaa13b5bdf6607c

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
600
x-request-id
683303e368f5fba2f1e3c4f2b929f6f0
access-control-expose-headers
x-request-id, x-bamtech-region, date
content-encoding
gzip
age
150736
access-control-allow-methods
GET, POST, PUT, PATCH, DELETE, OPTIONS
x-bypass-cache
false
x-cache
Hit from cloudfront
x-amz-cf-id
t0EDdmJgK7QFDOJcQxVYZI1GHubpse6OrmQCsRO8w7H818h4z1-VPQ==
date
Sat, 05 Sep 2026 01:23:14 GMT
content-type
application/json
vary
origin
cache-control
s-maxage=31536000
access-control-allow-credentials
true
x-bamtech-region
eu-central-1
via
1.1 ede4657ca75ee1968129a6a3c26144b0.cloudfront.net (CloudFront)
access-control-allow-origin
https://abc7.com
x-amz-cf-pop
FRA56-P14
POST
H2
200
s29145413145012 Show response
sw88.go.com/b/ss/wdgotvkabcresponsive,wdgotvsecondaryresponsive/1/JS-2.27.0/
43 B
200 B
121ms
117ms
XHR
image/gif
63.140.62.210
Amazon.com
General
Full URL
https://sw88.go.com/b/ss/wdgotvkabcresponsive,wdgotvsecondaryresponsive/1/JS-2.27.0/s29145413145012
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
63.140.62.210 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ip-63-140-62-210.data.adobedc.net
Software
jag /
Resource Hash
a1ecbaed793a1f564c49c671f2dd0ce36f858534ef6d26b55783a06b884cc506
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
Content-Type
application/x-www-form-urlencoded
sec-ch-ua-mobile
?0

Response headers

etag
3841251526430851072-4613833872099113960
x-content-type-options
nosniff
expires
Sat, 05 Sep 2026 19:15:30 GMT
p3p
CP="This is not a P3P policy"
date
Sun, 06 Sep 2026 19:15:30 GMT
last-modified
Mon, 07 Sep 2026 19:15:30 GMT
vary
*
content-type
image/gif;charset=utf-8
strict-transport-security
max-age=31536000; includeSubDomains
cache-control
no-cache, no-store, max-age=0, no-transform, private
pragma
no-cache
access-control-allow-credentials
true
access-control-allow-origin
https://abc7.com
content-length
43
x-xss-protection
1; mode=block
server
jag
GET
H2
200
sodar2.js Show response
ep2.adtrafficquality.google/sodar/
21 KB
8 KB
370ms
122ms
Script
text/javascript
142.251.14.132
Google LLC
General
Full URL
https://ep2.adtrafficquality.google/sodar/sodar2.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.14.132 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f132.1e100.net
Software
sffe /
Resource Hash
1fced7b2a471cda6a17da299daf9f375bc9755fc3f00cdf2937f87c81ecdc10e
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
"1782180379989953"
report-to
{"group":"adspam-signals-scs","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/adspam-signals-scs"}]}
x-content-type-options
nosniff
expires
Sun, 06 Sep 2026 19:15:31 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sun, 06 Sep 2026 19:15:31 GMT
content-type
text/javascript
vary
Accept-Encoding
cache-control
private, max-age=3000
cross-origin-opener-policy
same-origin; report-to="adspam-signals-scs"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
7626
x-xss-protection
0
server
sffe
GET
H2
200
l10n.js
login.disney.com/en-US/US/DATG-OTV.KABC.WEB/ Frame 4730
510 KB
77 KB
108ms
107ms
Other
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/l10n.js
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
b98910052a35e717266061c19a4c04fe0398d939cd096a7c3a61bd44657ef727

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
cfe2f1d9e7cf19d8f2f86230302b444e
cache-control
public, s-maxage=900, max-age=0, must-revalidate, stale-while-revalidate=60, stale-if-error=900, public, max-age=21600, stale-while-revalidate=86400, stale-if-error=86400
content-encoding
gzip
age
631
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
eRB_4AStKwiuZ4VuOuux7C7WCEumP2E_kGXY9RjShOmYYj5UMLzM2Q==
date
Sun, 06 Sep 2026 19:04:59 GMT
content-type
application/javascript; charset=utf-8
vary
Accept-Encoding,RSC
x-amz-cf-pop
FRA56-P10
GET
H2
200
esp Show response
rtb.openx.net/
Redirect Chain
  • https://rtb.openx.net/esp?url=https%3A%2F%2Fabc7.com%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F&rid=esp
  • https://rtb.openx.net/esp?url=https%3A%2F%2Fabc7.com%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F&rid=esp&cc=1
85 B
175 B
122ms
121ms
Fetch
application/json
35.227.252.103
Google LLC
General
Full URL
https://rtb.openx.net/esp?url=https%3A%2F%2Fabc7.com%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F&rid=esp&cc=1
Protocol
H2
Server
35.227.252.103 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
103.252.227.35.bc.googleusercontent.com
Software
/
Resource Hash
b8d88cf872440e7337710d0c2e6daddfa7be7fb34af7facb03c1e989822ebea2

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
Referer
https://abc7.com/

Response headers

cache-control
private, max-age=0, no-cache
x-forwarded-for
187.15.128.65
access-control-allow-credentials
true
via
1.1 google
access-control-allow-origin
https://abc7.com
alt-svc
h3=":443"; ma=2592000
content-length
85
date
Sun, 06 Sep 2026 19:15:30 GMT
content-type
application/json
vary
Origin

Redirect headers

cache-control
private, max-age=0, no-cache, must-revalidate
location
/esp?url=https%3A%2F%2Fabc7.com%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F&rid=esp&cc=1
pragma
no-cache
x-forwarded-for
187.15.128.65
access-control-allow-credentials
true
via
1.1 google
access-control-allow-origin
https://abc7.com
alt-svc
h3=":443"; ma=2592000
content-length
0
date
Sun, 06 Sep 2026 19:15:30 GMT
vary
Origin
GET
H2
200
Bootstrap.js Show response
dcf.espn.com/TWDC-DTCI/oneid_stage/ Frame 4730
73 KB
21 KB
415ms
177ms
Script
application/javascript
3.124.173.63
Amazon.com
General
Full URL
https://dcf.espn.com/TWDC-DTCI/oneid_stage/Bootstrap.js
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/6540-fc8e03091efbb1c6.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
3.124.173.63 Frankfurt am Main, Germany, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-3-124-173-63.eu-central-1.compute.amazonaws.com
Software
CloudFront /
Resource Hash
f259f87a130a3b7b0dde09703a6b86a5d2ecf3558d1f38c6c1b0deca1826533a

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-amz-version-id
PSSv5WCGmk.oHKjn20ML3MTcyWKYoBBs
etag
W/"d83e7ee6d4ee5134006dea8d01ffa87e"
age
5009634
alt-svc
h3=":443"; ma=86400
x-cache
Hit from cloudfront
x-amz-cf-id
0nKkALh7q97K9oAT7yuY-Xbu1SS9clcyxs0FQ_i43jHFKpJz_EEYNQ==
date
Sun, 06 Sep 2026 19:15:31 GMT
content-type
application/javascript; charset=utf-8
vary
Accept-Encoding, Origin
last-modified
Fri, 10 Jul 2026 19:41:09 GMT
x-amz-replication-status
COMPLETED
cache-control
max-age=300
via
1.1 4a0b7683a1d33d6d186965e831f2de96.cloudfront.net (CloudFront)
x-amz-cf-pop
FRA56-P7
server
CloudFront
x-amz-server-side-encryption
AES256
GET

18509950_1280X720-ABC7-LOS-ANGELES.jpg
cdn.abcotvs.com/dip/images/
0
0


GET
H2
200
siteconfig.js
login.disney.com/en-US/US/DATG-OTV.KABC.WEB/ Frame 4730
24 KB
6 KB
108ms
108ms
Other
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/siteconfig.js
Requested by
Host: login.disney.com
URL: https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
428a4999f41763e30da3413947d7fc44dc8aa24339b219c1bd685c5d6f83783b

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
5a6412313d4c00c98605eb472dc37df8
cache-control
public, s-maxage=900, max-age=0, must-revalidate, stale-while-revalidate=60, stale-if-error=900, public, max-age=21600, stale-while-revalidate=86400, stale-if-error=86400
content-encoding
gzip
age
254
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
mGOqULu_ptLYRTI_7l90GWPi1oKWEyovtCcdYF09HZhKTGkBlS53pg==
date
Sun, 06 Sep 2026 19:11:16 GMT
content-type
application/javascript; charset=utf-8
vary
Accept-Encoding,RSC
x-amz-cf-pop
FRA56-P10
GET

c232286c-0fba-467b-9cbb-768c343be8b1
https://login.disney.com/ Frame 4730
0
0


GET
H2
200
interaction Show response
login.disney.com/en-US/US/DATG-OTV.KABC.WEB/ Frame 4730
7 KB
3 KB
107ms
107ms
Fetch
text/x-component
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction?_rsc=193yh
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/4170-dd4027ed6752dacf.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
f43d92941ce27de9563e33f14e8554833d686b7690ebcc05b919e49e62d4c3ee

Request headers

RSC
1
sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
Next-Router-State-Tree
%5B%22%22%2C%7B%22children%22%3A%5B%5B%22lang%22%2C%22en-US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22countryCode%22%2C%22US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22clientId%22%2C%22DATG-OTV.KABC.WEB%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%22v5%22%2C%7B%22children%22%3A%5B%22bridge%22%2C%7B%22children%22%3A%5B%22web%22%2C%7B%22children%22%3A%5B%22__PAGE__%22%2C%7B%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%2Ctrue%5D
Next-Url
/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
x-deployment-id
51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249

Response headers

x-request-id
cdf37f4d40d22e58972468c3108aa270
cache-control
public, s-maxage=900, max-age=0, must-revalidate, stale-while-revalidate=60, stale-if-error=900
content-encoding
gzip
age
671
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
YaFSX98KEP7tSvu16OTkxP6DMz552Z1fNt1KU6Hx3CouFdiFVOWGbA==
date
Sun, 06 Sep 2026 19:04:19 GMT
content-type
text/x-component
vary
RSC,Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
account-picker Show response
login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/ Frame 4730
6 KB
3 KB
110ms
109ms
Fetch
text/x-component
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/account-picker?_rsc=193yh
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/4170-dd4027ed6752dacf.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
a22b9ac55c69bc876c7ba4fc1f7343bb6aee766b15f71839822232611f2c8a74

Request headers

RSC
1
sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
Next-Router-State-Tree
%5B%22%22%2C%7B%22children%22%3A%5B%5B%22lang%22%2C%22en-US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22countryCode%22%2C%22US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22clientId%22%2C%22DATG-OTV.KABC.WEB%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%22v5%22%2C%7B%22children%22%3A%5B%22bridge%22%2C%7B%22children%22%3A%5B%22web%22%2C%7B%22children%22%3A%5B%22__PAGE__%22%2C%7B%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%2Ctrue%5D
Next-Url
/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
x-deployment-id
51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249

Response headers

x-request-id
f7c3fded23e2e3ead8ff02d4b18cbe57
cache-control
public, s-maxage=900, max-age=0, must-revalidate, stale-while-revalidate=60, stale-if-error=900
content-encoding
gzip
age
671
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
mZ8Kz6ifpimLkPL6hLLL14zJLavzFdpi29k5WESo-1ypxJ5z_XznHQ==
date
Sun, 06 Sep 2026 19:04:19 GMT
content-type
text/x-component
vary
RSC,Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
error Show response
login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/biometrics/ Frame 4730
6 KB
3 KB
110ms
108ms
Fetch
text/x-component
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/biometrics/error?_rsc=193yh
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/4170-dd4027ed6752dacf.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
9bf2aa771861bd010888e75a81feeef0ba77df061db6225b4276e623749a1ed5

Request headers

RSC
1
sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
Next-Router-State-Tree
%5B%22%22%2C%7B%22children%22%3A%5B%5B%22lang%22%2C%22en-US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22countryCode%22%2C%22US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22clientId%22%2C%22DATG-OTV.KABC.WEB%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%22v5%22%2C%7B%22children%22%3A%5B%22bridge%22%2C%7B%22children%22%3A%5B%22web%22%2C%7B%22children%22%3A%5B%22__PAGE__%22%2C%7B%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%2Ctrue%5D
Next-Url
/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
x-deployment-id
51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249

Response headers

x-request-id
915f3a33f034e0413f216babb8682a8f
cache-control
public, s-maxage=900, max-age=0, must-revalidate, stale-while-revalidate=60, stale-if-error=900
content-encoding
gzip
age
671
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
8_ExGCbflaQcb7ZiHDENu2vPEVzOAf6M2zk60dMibUEHvkysZVyuhA==
date
Sun, 06 Sep 2026 19:04:19 GMT
content-type
text/x-component
vary
RSC,Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
consent Show response
login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/ Frame 4730
6 KB
3 KB
110ms
109ms
Fetch
text/x-component
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/consent?_rsc=193yh
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/4170-dd4027ed6752dacf.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
4dc758cb74b7155d91dd5c5401473189176558dd98ffbc4c64c209c30e607c85

Request headers

RSC
1
sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
Next-Router-State-Tree
%5B%22%22%2C%7B%22children%22%3A%5B%5B%22lang%22%2C%22en-US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22countryCode%22%2C%22US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22clientId%22%2C%22DATG-OTV.KABC.WEB%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%22v5%22%2C%7B%22children%22%3A%5B%22bridge%22%2C%7B%22children%22%3A%5B%22web%22%2C%7B%22children%22%3A%5B%22__PAGE__%22%2C%7B%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%2Ctrue%5D
Next-Url
/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
x-deployment-id
51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249

Response headers

x-request-id
8a18e21586de44c9323f4be76af1dab1
cache-control
public, s-maxage=900, max-age=0, must-revalidate, stale-while-revalidate=60, stale-if-error=900
content-encoding
gzip
age
671
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
gSLx-ByUQIzoF3dY5vS83gc0VS5LPD5qyLsCTcaZAT035Wi5NDIF5g==
date
Sun, 06 Sep 2026 19:04:19 GMT
content-type
text/x-component
vary
RSC,Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
device Show response
login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/ Frame 4730
6 KB
3 KB
110ms
109ms
Fetch
text/x-component
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/device?_rsc=193yh
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/4170-dd4027ed6752dacf.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
76ff9a86c4364bea10e7387ac2ec3f68edbe4a047693171f2c69029f8b0a9daa

Request headers

RSC
1
sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
Next-Router-State-Tree
%5B%22%22%2C%7B%22children%22%3A%5B%5B%22lang%22%2C%22en-US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22countryCode%22%2C%22US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22clientId%22%2C%22DATG-OTV.KABC.WEB%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%22v5%22%2C%7B%22children%22%3A%5B%22bridge%22%2C%7B%22children%22%3A%5B%22web%22%2C%7B%22children%22%3A%5B%22__PAGE__%22%2C%7B%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%2Ctrue%5D
Next-Url
/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
x-deployment-id
51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249

Response headers

x-request-id
ffed34e8f3afcf20e1daa69604eae40d
cache-control
public, s-maxage=900, max-age=0, must-revalidate, stale-while-revalidate=60, stale-if-error=900
content-encoding
gzip
age
671
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
U9a519f4LLXZ4a88JZwxsEKtvb-xtpYuRIcf1_Rqw9RPxtIbxG9LEA==
date
Sun, 06 Sep 2026 19:04:19 GMT
content-type
text/x-component
vary
RSC,Accept-Encoding
x-amz-cf-pop
FRA56-P10
OPTIONS

wsg
27f19c7c68e3eadf7756fb7efdb661dd8909acf9.ipv4.cws.conviva.com/0/ Frame
0
0


OPTIONS

wsg
27f19c7c68e3eadf7756fb7efdb661dd8909acf9.ipv6.cws.conviva.com/0/ Frame
0
0


POST

wsg
27f19c7c68e3eadf7756fb7efdb661dd8909acf9.ipv4.cws.conviva.com/0/
0
0


POST

wsg
27f19c7c68e3eadf7756fb7efdb661dd8909acf9.ipv6.cws.conviva.com/0/
0
0


GET
H2
200
playback-session.js Show response
hiveplayer-static.bamgrid.com/artifacts/hive/playback-session/26.10.1-jasmine/all_browser_es5/
2 MB
498 KB
126ms
125ms
Script
application/javascript
99.84.152.107
Amazon.com
General
Full URL
https://hiveplayer-static.bamgrid.com/artifacts/hive/playback-session/26.10.1-jasmine/all_browser_es5/playback-session.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
99.84.152.107 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-99-84-152-107.fra56.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
783a22a2f97193975e040f4ae8d071515e3df8773c0564207a79e8aa99416807

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-encoding
gzip
etag
W/"1cf629716ca38b3f65bfc2e6b7b264d7"
x-amz-version-id
GDs_qy6etElQA2caCJhDjF2b4T17K_Qe
age
59
via
1.1 2694fffaa67bb0ec65670b8dce8dcd24.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
Q7IcrhwDr1F9p6Jf4kMM3pEeSwYm5StogAaOAgoLXqID1ByS_9Z2yA==
date
Sun, 06 Sep 2026 19:14:33 GMT
content-type
application/javascript
last-modified
Fri, 04 Sep 2026 14:25:47 GMT
server
AmazonS3
x-amz-cf-pop
FRA56-P13
x-amz-server-side-encryption
AES256
GET
H2
200
s26339666390344
sw88.go.com/b/ss/wdgotvkabcresponsive,wdgotvsecondaryresponsive/1/JS-2.27.0/
43 B
122 B
114ms
113ms
Image
image/gif
63.140.62.210
Amazon.com
General
Full URL
https://sw88.go.com/b/ss/wdgotvkabcresponsive,wdgotvsecondaryresponsive/1/JS-2.27.0/s26339666390344?AQB=1&ndh=1&pf=1&t=6%2F8%2F2026%2022%3A15%3A30%200%20-180&mid=54109714201665181872321563256462948945&aamlh=6&ce=UTF-8&ns=abcotv&pageName=disasters-accidents%2Fpost_video%2F34magnitude-earthquake-hits-ontario-area-shaking-felt-across-san-bernardino-county-usgs-says%3D19779712&g=https%3A%2F%2Fabc7.com%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F&c.&module_name=Top%20Stories&page_name=disasters-accidents%2Fpost_video%2F34magnitude-earthquake-hits-ontario-area-shaking-felt-across-san-bernardino-county-usgs-says%3D19779712&page_url=https%3A%2F%2Fabc7.com%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F&story_title=3.4-magnitude%20earthquake%20hits%20Ontario%20area%2C%20shaking%20felt%20across%20San%20Bernardino%20County%2C%20USGS%20says&event_name=module%20impression&placement=right%20rail&creative_type=content&.c&server=kabc&pe=lnk_o&pev2=module%20impression&s=1600x1200&c=24&j=1.6&v=N&k=Y&bw=1600&bh=1200&mcorgid=19916ABB53224B2C0A490D45%40AdobeOrg&AQE=1
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
63.140.62.210 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ip-63-140-62-210.data.adobedc.net
Software
jag /
Resource Hash
a1ecbaed793a1f564c49c671f2dd0ce36f858534ef6d26b55783a06b884cc506
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
no-cache, no-store, max-age=0, no-transform, private
pragma
no-cache
etag
3841251527050002432-4613866131596257610
x-content-type-options
nosniff
expires
Sat, 05 Sep 2026 19:15:30 GMT
access-control-allow-origin
*
p3p
CP="This is not a P3P policy"
content-length
43
date
Sun, 06 Sep 2026 19:15:30 GMT
x-xss-protection
1; mode=block
last-modified
Mon, 07 Sep 2026 19:15:30 GMT
vary
*
server
jag
content-type
image/gif;charset=utf-8
GET
H2
200
recaptcha__iw.js Show response
www.gstatic.com/recaptcha/releases/8x-4t2pegToiW8KmThtO4AQt/ Frame 4730
830 KB
348 KB
360ms
113ms
Script
text/javascript
142.250.154.94
Google LLC
General
Full URL
https://www.gstatic.com/recaptcha/releases/8x-4t2pegToiW8KmThtO4AQt/recaptcha__iw.js
Requested by
Host: www.google.com
URL: https://www.google.com/recaptcha/enterprise.js?render=6LcnzusZAAAAABiX7zUG2lN9BBH_1ERH1pfyR95-
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.250.154.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bt-in-f94.1e100.net
Software
sffe /
Resource Hash
67da984086b5b0d6fa498f8b125d3bac45ef9f195172a0bee43a52755c80718f
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://login.disney.com
sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
age
431943
report-to
{"group":"recaptcha-scs","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/recaptcha-scs"}]}
x-content-type-options
nosniff
expires
Wed, 01 Sep 2027 19:16:28 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Tue, 01 Sep 2026 19:16:28 GMT
last-modified
Mon, 31 Aug 2026 04:01:33 GMT
content-type
text/javascript
vary
Accept-Encoding
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin-allow-popups; report-to="recaptcha-scs"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/recaptcha-scs
accept-ranges
bytes
access-control-allow-origin
*
content-length
355787
x-xss-protection
0
server
sffe
GET
H3
200
css2
fonts.googleapis.com/
4 KB
616 B
247ms
124ms
Stylesheet
text/css
142.251.14.95
Google LLC
General
Full URL
https://fonts.googleapis.com/css2?family=Montserrat:ital,wght@0,400;0,600&display=swap
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H3
Security
QUIC, , AES_256_GCM
Server
142.251.14.95 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f95.1e100.net
Software
ESF /
Resource Hash
3d64cd245df1076827c2966fe331cff41825028484305357264ebe5d037dbc37
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-content-type-options
nosniff
expires
Sun, 06 Sep 2026 19:15:31 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sun, 06 Sep 2026 19:15:31 GMT
content-type
text/css; charset=utf-8
vary
Sec-Fetch-Dest, Sec-Fetch-Mode, Sec-Fetch-Site
last-modified
Sun, 06 Sep 2026 18:58:18 GMT
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=31536000
link
<https://fonts.gstatic.com>; rel=preconnect; crossorigin
cache-control
private, max-age=86400, stale-while-revalidate=604800
timing-allow-origin
*
cross-origin-opener-policy
same-origin-allow-popups
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
x-xss-protection
0
server
ESF
GET
H2
200
log Show response
log.go.com/
1 B
342 B
189ms
189ms
Fetch
application/octet-stream
15.197.135.246
Amazon.com
General
Full URL
https://log.go.com/log?appid=IDENTITY-SDK-V5&sdk_version=web+5.1.30-qa.0&conversation_id=b93d8c77-0419-4d26-8071-b0080456f1ad&language=en-US&sdk_install_id=2627c924-96e2-4c09-a5ce-389cc2d6003e&detected_country=US&swid=76d9eb61-6562-4b6d-a09d-8ea2b1296ac4&event_start_time=1788722130606&request_id=04a305cdc7c32f99fe998f90da2896b1&transaction_id=76c01acc-7e3c-40c8-92fd-7066d9a91c52&action_name=service%3Adevice%3Aregister&process_time=344&client_id=DATG-OTV.KABC.WEB-PROD&timestamp=1788722130951
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
15.197.135.246 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
a7b7d02f3736e735c.awsglobalaccelerator.com
Software
/
Resource Hash
36a9e7f1c95b82ffb99743e0c5c4ce95d83c9a430aac59f84ef3cbfab6145068

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
900
cache-control
no-cache
pragma
no-cache
access-control-allow-credentials
true
access-control-allow-methods
GET, POST, OPTIONS
allow
GET, OPTIONS
expires
0
access-control-allow-origin
https://abc7.com
date
Sun, 06 Sep 2026 19:15:31 GMT
content-type
application/octet-stream
vary
Origin
GET
H2
200
log Show response
log.go.com/
1 B
342 B
190ms
190ms
Fetch
application/octet-stream
15.197.135.246
Amazon.com
General
Full URL
https://log.go.com/log?appid=IDENTITY-SDK-V5&sdk_version=web+5.1.30-qa.0&conversation_id=cd427a9a-db6d-4f42-94c5-7de524af8ce9&language=en-US&sdk_install_id=2627c924-96e2-4c09-a5ce-389cc2d6003e&detected_country=US&swid=76d9eb61-6562-4b6d-a09d-8ea2b1296ac4&event_start_time=1788722130606&info=registered%28true%29%2Cskipped%28false%29%2Cstrategy%28unifiedRegister%29&action_name=log%3Adevice%3Aregister&process_time=345&client_id=DATG-OTV.KABC.WEB-PROD&timestamp=1788722130952
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
15.197.135.246 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
a7b7d02f3736e735c.awsglobalaccelerator.com
Software
/
Resource Hash
36a9e7f1c95b82ffb99743e0c5c4ce95d83c9a430aac59f84ef3cbfab6145068

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
900
cache-control
no-cache
pragma
no-cache
access-control-allow-credentials
true
access-control-allow-methods
GET, POST, OPTIONS
allow
GET, OPTIONS
expires
0
access-control-allow-origin
https://abc7.com
date
Sun, 06 Sep 2026 19:15:31 GMT
content-type
application/octet-stream
vary
Origin
GET
H2
200
log Show response
log.go.com/
1 B
342 B
190ms
189ms
Fetch
application/octet-stream
15.197.135.246
Amazon.com
General
Full URL
https://log.go.com/log?appid=IDENTITY-SDK-V5&sdk_version=web+5.1.30-qa.0&conversation_id=607d8b53-518a-48fa-8c89-800ac52270d9&language=en-US&sdk_install_id=2627c924-96e2-4c09-a5ce-389cc2d6003e&detected_country=US&device_id=01a07825-af7b-7531-9039-34c597cd9d53&swid=76d9eb61-6562-4b6d-a09d-8ea2b1296ac4&event_start_time=1788722129688&info=initparams%28prod%2CDATG-OTV.KABC.WEB%2Cen-US%29&action_name=flow%3Ainitialization&process_time=1264&client_id=DATG-OTV.KABC.WEB-PROD&timestamp=1788722130952
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
15.197.135.246 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
a7b7d02f3736e735c.awsglobalaccelerator.com
Software
/
Resource Hash
36a9e7f1c95b82ffb99743e0c5c4ce95d83c9a430aac59f84ef3cbfab6145068

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
900
cache-control
no-cache
pragma
no-cache
access-control-allow-credentials
true
access-control-allow-methods
GET, POST, OPTIONS
allow
GET, OPTIONS
expires
0
access-control-allow-origin
https://abc7.com
date
Sun, 06 Sep 2026 19:15:31 GMT
content-type
application/octet-stream
vary
Origin
GET
H3
200
adview
securepubads.g.doubleclick.net/pagead/ Frame 595B
0
0
196ms
196ms
Fetch
text/html
142.250.154.154
Google LLC
General
Full URL
https://securepubads.g.doubleclick.net/pagead/adview?ai=CY81f0rudaoDxJP-EmNAP7LajwAac3IGXhwHf1JOirRbAjbcBEAEgkvrgb2D5uvSDnBDIAQngAgCoAwHIAwKqBIADT9CNMjjqNnztRarE9rPkInz6pLvZxn_yHLOM6z-idDO-8_qr7Mmg9elX8XHlwCyJhx4h7-1tLgNcL6H6TET1nMvlaZKjeZdyeatzrsbgq6p1jm7XTLXpznA0PKvDdiIIFo9n6BXphze_9-9ZJfmxPUM0iT4FWr-SLj7ulpialfV9AVV-co_8OXs6Sb-d-fCJBB3StFOY1oythTdOxKEW1cG5NDYgXW4E5pXRnZ0loh1LkszRF0Gv8ByVzGwFLDzHbT-xfzQmPWxqxKA6G__-vqBU_Sqr18Qm7483OOs8g3DfD4OKfkZvfVStv9xrElcHcTTggHNcjFJw52k-2g1eteHkTXmABCVcnhdCbF5PpmEanE61g5NlRB5NkW48G_bKsSfp84j1rkV_3Z87D1EneHa8hLZ8RdWSWTyZ7asU4Xw_DGnF50ukdHJb5pVcxTAzqJSOaEscVXeLFwDjh4jRzZmcg53vPPc8t-2Q1yHZ1xdqyouuIDbo2XEFBxjToDDx4AQBgAavp5DL_8K4_UygBiGoB5PYsQKoB5TYsQKoB5XYsQKoB6a-G6gHltgbqAeqm7ECqAf_nrECqAffn7ECqAf-6LECqAetvrEC2AcA0ggwCIBhEAEyCIqCgICAgIAIOg-AQIDAgICAgKiAAqiDkBBIvf3BOljuzMaZ1dqWA2AAgAoD-gsCCAGADAGqDQJJTOINEwjmoseZ1dqWAxV_AgYEHWzbCGjqDRMI44PImdXalgMVfwIGBB1s2whoiA7___________8B0BUBgBcBshcsChoSFHB1Yi03MTU0ODc5NjUxOTkyNjIxGNvHbxgMKgo0MDM2NjAxMTMwUAGqGBcJ43oUrgdAv0ASCjQwMzY2MDExMzAYAQ&sigh=LA2IjG5HxsQ&uach_m=%5BUACH%5D&sreq=1&cid=CAQShwIAQM4h3PIgp1aO-yYQmCiFcqHJ7Z_e9ztBjXcKcmDzfvPwRD_Pqp8LeiCksp5dFpuzWGKMV881n4dSmlA1OB6axy1On9oEERjGCN6ZpFZi9QMy88x105xTqM3Uj8qo3WLZh94tsdswcieENYt1ynlYp-A-7gYPnr9Y6S85ZktvqTyNY83ybGuvKxyZY7s9Kz59tQIs8PB5cpzCDu8ZWjyCciB8n1uEQuB6cZEBvL6Zq_hnFG-HfOLnMCgObBHTIuq4Cnr9MYrrz1BWrSJaiWbyel0pkSNd0IYcw4Qq7DQuZa2HBcj65J-0aqHWYjGBVR9hy6qHqUbMnqPxmm0TR127W6BTGKy2hhgB
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.250.154.154 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bt-in-f154.1e100.net
Software
/
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

GET
H2
200
T0ZHVb0CAAAAAAAAeJxNks1v0mAAh-lARGLMwglv0ygxZgzavoV2CZlvWygF1tJubLy9NO1o3_JVoC2fxmQmHrzp2aMHY-Kf4WVXjYd58l_wpFencdHf6Tn-8uRJb1LxbSJL3Iv92feDR59__viSpO4D-symy8Vi3qJtwLJOKc9RrMsUS_mS5TI0x7gsEdxKXarbl...
eu.asas.yango.com/ex-event/ Frame 595B
0
0
457ms
150ms
Fetch
45.87.133.75
TELETECH Edge Tec...
General
Full URL
https://eu.asas.yango.com/ex-event/T0ZHVb0CAAAAAAAAeJxNks1v0mAAh-lARGLMwglv0ygxZgzavoV2CZlvWygF1tJubLy9NO1o3_JVoC2fxmQmHrzp2aMHY-Kf4WVXjYd58l_wpFencdHf6Tn-8uRJb1LxbSJL3Iv92feDR59__viSpO4D-symy8Vi3qJtwLJOKc9RrMsUS_mS5TI0x7gsEdxKXarbl2r2Irn5h-dE7CVBvCa-vXj_7tXz8w_KGyKR2UoRb4k76XTqayITD60wG9tOZD7F0x_jXhRNw_1CwbLDvbXl95zVXjAvhOG04CwcPyqQB2cVFhRzTlShc26l2eAOGxjz8O-cxmYwV_JrNBqZiFVmbVBr0WWuhwwVcPWyykXtoBYyAarpmFRbGPHHeCjxR0gUjhgJaqjB444kakjkcSjxS0ODgggQ9DCWmhukujPYmTCH4xVnUpHrztt-CcxGK6xHed_QFl3aAdx6jfkaedw_qq6aStRrbUJWAXM9bNEKohumjHhT3zT6y-5aHEzHmq4CB-OmWBVs1PT6htTug_kAA0p27P5Kkq8eSaetoYUYQZfcCTM6odyewWtwWBT00w5kurjmyFKod2DZc3D9tCkbJwO4tqXaGLpj8WzZ9YwSFgctuXM8gMsuVjRFn6H6oLpcSPwwfyi28qi2WbsiqENp5p542kNKyE0rD57CjnAsq4rZ1mWh-ixnVebQ783wEP7v27hSJJoIQn_Iq9rubuam1Q_MXjjNJu5ed7RzkSSvmbuGJ7F6zBCyWzvE46Rt-b4TULdJjiUBxVKAZGjqRjSJrNF-Ug4DyxnxWc8KTbvfMy17snB-kzuaTAKTtK968ohfMqrU_A,,?pr=ap270gAJOIAEBgJ_AAjbbEyyaFx6hhR6Gr4Bng
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
45.87.133.75 , Serbia, ASN208398 (TELETECH Edge Technology Plus d.o.o. Beograd, RS),
Reverse DNS
Software
/
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-yt-trace-id
6993fded-bc20e2a9-9fd6c29f-20373311
x-yt-request-id
669327a7-cb73177-1cbeee1a-76b1d4ba
content-length
0
GET
H2
200
air_adaptive.css
display.asas.yango.tech/ver/155/ Frame 595B
18 KB
5 KB
405ms
130ms
Stylesheet
text/css
212.102.56.178
CDN77 Datacamp Li...
General
Full URL
https://display.asas.yango.tech/ver/155/air_adaptive.css
Requested by
Host: scripts.webcontentassessor.com
URL: https://scripts.webcontentassessor.com/scripts/fea4ac1291b1ab4b9e08331b030dbfca29ba761aae7f184704ffd867755688c0
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
212.102.56.178 Frankfurt am Main, Germany, ASN60068 (CDN77 Datacamp Limited, GB),
Reverse DNS
245149724.fra.cdn77.com
Software
CDN77-Turbo /
Resource Hash
719453dc3943f1b9706f308913e37b43ff7026e02fef3f238e6f2c45dd1d3bf1
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
35fe934f8c53f389
content-encoding
gzip
etag
W/"74119611347aec97036793bb790e2eac"
age
100
x-77-cache
HIT
x-content-type-options
nosniff
x-amz-cf-id
f4fSJwEZYVRhFzNx_bZRgZi9U3WVwLu1Rv_wDYBbwQPwonpeLYqXQg==
date
Sun, 06 Sep 2026 19:15:31 GMT
content-type
text/css
last-modified
Fri, 28 Aug 2026 07:16:50 GMT
vary
Accept-Encoding
cache-host
cloudcdn-fra-01.cdn.yandex.net
strict-transport-security
max-age=31536000
x-77-nzt
kjAc0zgIf9UNZiUBWohjyEmBN85wYXamA5sddTxyr7JMn+3A7wy+ppA
cache-control
max-age=345600
x-77-nzt-ray
1cb09c0ed81c8ad5f8bb9d6af915c116
via
1.1 db863971352ff4860373667d6300f00a.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-77-pop
frankfurtDE
x-strm-log-split
3
cache-status
MISS
x-77-age
211771
x-amz-cf-pop
FRA56-P13
server
CDN77-Turbo
GET
H2
200
air_adaptive.js Show response
display.asas.yango.tech/ver/155/ Frame 595B
504 KB
154 KB
360ms
109ms
Script
text/javascript
212.102.56.178
CDN77 Datacamp Li...
General
Full URL
https://display.asas.yango.tech/ver/155/air_adaptive.js
Requested by
Host: scripts.webcontentassessor.com
URL: https://scripts.webcontentassessor.com/scripts/fea4ac1291b1ab4b9e08331b030dbfca29ba761aae7f184704ffd867755688c0
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
212.102.56.178 Frankfurt am Main, Germany, ASN60068 (CDN77 Datacamp Limited, GB),
Reverse DNS
245149724.fra.cdn77.com
Software
CDN77-Turbo /
Resource Hash
0f5d73f6ef18deb3c793b7af7e740e809287a55766326d89501a7e03638f4715
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff

Request headers

Origin
https://abc7.com
sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
f9b25a1ff0f1fae2
content-encoding
gzip
etag
W/"14fdbce6aac7d7015321ca24efb87048"
age
100
x-77-cache
HIT
x-content-type-options
nosniff
x-amz-cf-id
nygKB16sCFzRHhxU55oRTX4JMxrtcUEW-q5hUGaOYwIiUtc-qquYyw==
date
Sun, 06 Sep 2026 19:15:31 GMT
content-type
text/javascript
last-modified
Fri, 28 Aug 2026 07:16:50 GMT
vary
Accept-Encoding
cache-host
cloudcdn-fra-01.cdn.yandex.net
strict-transport-security
max-age=31536000
x-77-nzt
ksJi83Ay6Q+NeEd7qBz6V/QLEmsaHJ8EKbi/w1OxQrD4JHhO7mqo0fU
cache-control
max-age=345600
x-77-nzt-ray
1cb09c0e3f52f8d3f8bb9d6a72a4ff13
via
1.1 a456f20879ae2a7f67cd26298f7cded0.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-77-pop
frankfurtDE
x-strm-log-split
1
cache-status
MISS
x-77-age
211784
x-amz-cf-pop
FRA56-P13
server
CDN77-Turbo
GET
H2
200
window_focus_fy2021.js Show response
tpc.googlesyndication.com/pagead/js/r20260902/r20110914/client/ Frame 595B
3 KB
1 KB
362ms
121ms
Script
text/javascript
142.251.14.132
Google LLC
General
Full URL
https://tpc.googlesyndication.com/pagead/js/r20260902/r20110914/client/window_focus_fy2021.js
Requested by
Host: scripts.webcontentassessor.com
URL: https://scripts.webcontentassessor.com/scripts/fea4ac1291b1ab4b9e08331b030dbfca29ba761aae7f184704ffd867755688c0
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.14.132 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f132.1e100.net
Software
cafe /
Resource Hash
6866f5af8889d6c11bd994ef35abef4e520ad362671ede3485b9005baeef9a53
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
etag
8676712673563253577
age
40095
x-content-type-options
nosniff
expires
Sun, 20 Sep 2026 08:07:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
date
Sun, 06 Sep 2026 08:07:16 GMT
content-disposition
attachment; filename="f.txt"
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
cache-control
public, max-age=1209600
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
content-length
1227
x-xss-protection
0
server
cafe
GET
H2
200
qs_click_protection_fy2021.js Show response
tpc.googlesyndication.com/pagead/js/r20260902/r20110914/client/ Frame 595B
21 KB
9 KB
355ms
114ms
Script
text/javascript
142.251.14.132
Google LLC
General
Full URL
https://tpc.googlesyndication.com/pagead/js/r20260902/r20110914/client/qs_click_protection_fy2021.js
Requested by
Host: scripts.webcontentassessor.com
URL: https://scripts.webcontentassessor.com/scripts/fea4ac1291b1ab4b9e08331b030dbfca29ba761aae7f184704ffd867755688c0
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.14.132 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f132.1e100.net
Software
cafe /
Resource Hash
7a6a23e219213f553a3b8a3d0971423efeb6f98adaad39270aa26bb44c3a3bf5
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
etag
15652905145164729613
age
40095
x-content-type-options
nosniff
expires
Sun, 20 Sep 2026 08:07:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
date
Sun, 06 Sep 2026 08:07:16 GMT
content-disposition
attachment; filename="f.txt"
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
cache-control
public, max-age=1209600
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
content-length
8670
x-xss-protection
0
server
cafe
GET
H2
200
ext.js Show response
tpc.googlesyndication.com/safeframe/1-0-45/js/ Frame 595B
23 KB
6 KB
407ms
167ms
Script
text/javascript
142.251.14.132
Google LLC
General
Full URL
https://tpc.googlesyndication.com/safeframe/1-0-45/js/ext.js
Requested by
Host: scripts.webcontentassessor.com
URL: https://scripts.webcontentassessor.com/scripts/fea4ac1291b1ab4b9e08331b030dbfca29ba761aae7f184704ffd867755688c0
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.14.132 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f132.1e100.net
Software
sffe /
Resource Hash
4c95e84767aed248594e7d485707c7ed904fd2fe4ec3ea98687fc2de59ddf231
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
report-to
{"group":"ads-gpt-scs","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/ads-gpt-scs"}]}
x-content-type-options
nosniff
expires
Sun, 06 Sep 2026 19:15:31 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sun, 06 Sep 2026 19:15:31 GMT
content-type
text/javascript
vary
Accept-Encoding
last-modified
Thu, 08 May 2025 23:15:48 GMT
cache-control
private, max-age=300
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
cross-origin-opener-policy-report-only
same-origin; report-to="ads-gpt-scs"
content-length
6269
x-xss-protection
0
server
sffe
GET
H3
200
ufs_web_display.js Show response
pagead2.googlesyndication.com/pagead/managed/js/activeview/current/ Frame 595B
239 KB
74 KB
235ms
113ms
Script
text/javascript
142.251.127.157
Google LLC
General
Full URL
https://pagead2.googlesyndication.com/pagead/managed/js/activeview/current/ufs_web_display.js
Requested by
Host: scripts.webcontentassessor.com
URL: https://scripts.webcontentassessor.com/scripts/fea4ac1291b1ab4b9e08331b030dbfca29ba761aae7f184704ffd867755688c0
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.127.157 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfrai-in-f157.1e100.net
Software
cafe /
Resource Hash
5b0d6fda9d4c1601d352e39f939162c2e95e547915536847e3782a0a10dfd92d
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
etag
2640385400941753791
age
2783
x-content-type-options
nosniff
expires
Sun, 06 Sep 2026 19:29:08 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
date
Sun, 06 Sep 2026 18:29:08 GMT
content-disposition
attachment; filename="f.txt"
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
cache-control
public, max-age=3600, stale-while-revalidate=3600
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
content-length
75325
x-xss-protection
0
server
cafe
GET
H2
200
log Show response
log.go.com/ Frame 4730
1 B
347 B
568ms
191ms
Fetch
application/octet-stream
3.33.135.48
Amazon.com
General
Full URL
https://log.go.com/log?level=30&appid=IDENTITY-SDK-V5&lightbox_version=1.0.830&sdk_version=5.1.30-qa.0&platform=web&git_sha=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249&install_id=bfe39624-1c94-4fde-9cb9-d389424bddfc&environment=prod&client_id=DATG-OTV.KABC.WEB-PROD&country_code=us&language=en-us&view=v5%2Fbridge%2Fweb&action_name=view%3Aweb&device_time=1788722131042&timestamp=1788722131042&oidc_classification_code=FIRST_PARTY&source=identity+sdk+v5&conversation_id=7e1df8d8-bd78-4f23-9863-277becde8879&device_id=01a07825-af7b-7531-9039-34c597cd9d53&sdk_install_id=2627c924-96e2-4c09-a5ce-389cc2d6003e&bu_name=&client_context=&swid=76d9eb61-6562-4b6d-a09d-8ea2b1296ac4&rum_session_id=19025b3b-3d16-4e5c-aae7-7cb4eecd4141
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/4170-dd4027ed6752dacf.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
3.33.135.48 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
Software
/
Resource Hash
36a9e7f1c95b82ffb99743e0c5c4ce95d83c9a430aac59f84ef3cbfab6145068

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
accept
application/json
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
900
cache-control
no-cache
pragma
no-cache
access-control-allow-credentials
true
access-control-allow-methods
GET, POST, OPTIONS
allow
GET, OPTIONS
expires
0
access-control-allow-origin
https://login.disney.com
date
Sun, 06 Sep 2026 19:15:31 GMT
content-type
application/octet-stream
vary
Origin
POST
H2
200
map Show response
bcp.crwdcntrl.net/6/
235 B
691 B
400ms
138ms
XHR
application/json
108.129.59.25
Amazon.com
General
Full URL
https://bcp.crwdcntrl.net/6/map?xcid=16589
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
108.129.59.25 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-108-129-59-25.eu-west-1.compute.amazonaws.com
Software
/
Resource Hash
f817cdbc962eb7efed5865a20e61dc370b5b9509ba60b8997ba1e21f92d0cc9b
Security Headers
Name Value
Strict-Transport-Security max-age=31536000 ; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000 ; includeSubDomains
cache-control
no-cache
pragma
no-cache
access-control-allow-credentials
true
expires
0
access-control-allow-origin
https://abc7.com
p3p
CP=NOI DSP COR NID PSAa PSDa OUR UNI COM NAV
content-length
235
date
Sun, 06 Sep 2026 19:15:31 GMT
content-type
application/json;charset=utf-8
GET
H2
204
sync Show response
spadsync.com/
0
75 B
259ms
121ms
XHR
text/plain
34.8.2.179
Google LLC
General
Full URL
https://spadsync.com/sync?sptoken=f95c3132-3c5c-43bd-a6b9-f8881460ff64&sspid=GgL&pubid=googless&ssphost=abc7.com&sharedId=df51ba04-28ed-4136-90b1-20f856942db0
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.8.2.179 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
179.2.8.34.bc.googleusercontent.com
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

via
1.1 google
access-control-allow-origin
*
alt-svc
h3=":443"; ma=2592000
date
Sun, 06 Sep 2026 19:15:31 GMT
GET
H2
200
f4898fe8-aa54f69b7fcf3fc2.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
230 KB
53 KB
113ms
109ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/f4898fe8-aa54f69b7fcf3fc2.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
29edbb483a7da78ceda6566ce2faf1116d561d992efaf566aad91786c680bd57

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
3a5e7c12962cd8091ad8ee8ea31a62f6
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"396a9-1a01fc3c5d8"
age
1473341
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
ZdcNqnzJuBdNuxj3Zfj8fT6d2gjojrTjlB92Y1WFXk7nPeqM5_X6Rw==
date
Thu, 20 Aug 2026 17:59:50 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
3824-e44ac8a102e129c3.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
39 KB
13 KB
117ms
114ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/3824-e44ac8a102e129c3.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
2f6c4f3094860906163515266ba7d43b89690cb2a5a32ae3524cdcbb8cebbae6

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
9094b08cf6195d0c16b59945f3cf765f
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"9c48-1a01fc3c5d8"
age
1473341
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
AvSH1uK-6t38aba4PPayylHw-nKqMkzY7ffitxOwsvBnbALJOnhI-w==
date
Thu, 20 Aug 2026 17:59:50 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
5674-1a62b102d15b9892.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
6 KB
3 KB
118ms
115ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/5674-1a62b102d15b9892.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
5480e630bc419bb548e56e3149f9f687a00a7b0803302e84d92be06582aab92b

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
7f97a8074de27dfc6573a67884db5621
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"1731-1a01fc3c5d8"
age
1473341
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
prlV-Pt2fIv00X2lR-0sniq68GXZ3B45DQGQwZ2isnwXc2UQY90Xkw==
date
Thu, 20 Aug 2026 17:59:50 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
5479-775b98122073da64.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
8 KB
3 KB
118ms
115ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/5479-775b98122073da64.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
8faa033d529730e32cbed5ab73b8dcb6963dde710ad9cf46a5d5eb5b420c2f54

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
25cafeb02ee935e9d2d95a6e8301e7ba
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"1f80-1a01fc3c5d8"
age
1473341
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
2RtNR7AmDkBtKvltGQo-zBbwzhXqJK3v59ITF0L-XgagtFrK29jgHg==
date
Thu, 20 Aug 2026 17:59:50 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
3381-e8c39f53c9d660e5.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
16 KB
6 KB
119ms
116ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/3381-e8c39f53c9d660e5.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
caef0b2970645e1e41726b2233d4c4958cb061999e367b6688db14a879eb448f

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
7a605517df18a3d6c650c0a0dc41cd0f
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"3fd4-1a01fc3c5d8"
age
1473341
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
BI6vUGLXQqeL7BLgpwe5Kb5_4ex47EgACUI1aXNe21hhXAMPsdENGQ==
date
Thu, 20 Aug 2026 17:59:50 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
5364-991fd9414d5160f1.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
18 KB
7 KB
119ms
116ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/5364-991fd9414d5160f1.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
e438493dc939900a8bed78da367a78a6c034afa5ac195cbabf49ce21dc089a72

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
fdcdfbfc0821cdd541896cbcfed6039a
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"4936-1a01b947020"
age
959539
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
aM1qNISQRTc7gq4VnIM8pQvWWMBFdVThWbdojXH2Zq1oHrIieBBpvg==
date
Wed, 26 Aug 2026 16:43:12 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 19 Aug 2026 19:51:48 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
6128-e6f058539ee4463b.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
25 KB
10 KB
121ms
118ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/6128-e6f058539ee4463b.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
e7b35a5402bcc6ff5ed6ac9925a5f54633f762cd4bce9e6e1febc58002711506

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
490abe0c20b864ccd8ec39fe2c60c167
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"626d-1a01fc3c5d8"
age
1473341
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
VXzDyKtu6vXLz2iBivsmWtC_2q6LFDo36uO0W7G-RXEto9Z8ZJNPXA==
date
Thu, 20 Aug 2026 17:59:50 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
9457-846c515940e99d90.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
32 KB
9 KB
121ms
119ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/9457-846c515940e99d90.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
359c2507207443f123047dbf40c2fcdee434ae48704b53e94ab522c096f4cd0f

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
c47a260fef04fbe4e05a405afbc74d03
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"7fbc-1a01fc3c5d8"
age
1473341
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
igXiz6766YZ8Ylb3k_iktxdKLRMGzOf_hklQjXUI4qjB7scRuOaxew==
date
Thu, 20 Aug 2026 17:59:50 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
8107-a5fd7abd794a2fa2.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
12 KB
5 KB
122ms
119ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/8107-a5fd7abd794a2fa2.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
462a6d12bed8a1a91ae16f9bc30265f5d0ae2bfa0898be663e419b6983fd04ca

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
11c64d74f64cb999d037cf182f5981e9
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"2f95-1a01fc3c5d8"
age
1473341
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
jOcrRZ4QkagXUVbVaAv4KlKhrveQbzFjGHjTGsxCnY6uXeEt6VTVDw==
date
Thu, 20 Aug 2026 17:59:50 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
3867-5e8292673169ac50.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
20 KB
7 KB
122ms
119ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/3867-5e8292673169ac50.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
4f3132d2593617bb5fc83cd3039db0fa2d54d5477a91cb26251e8153e7bb9627

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
18333203202d06fe1801ff016afbb2ac
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"4ecd-1a05f957328"
age
266838
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
eJzDzO5UXuWfTMvxiZ0QyskHZJDiogAfq-XELyZL4azImHp5KXoIgw==
date
Thu, 03 Sep 2026 17:08:13 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
5583-26afedaf683dfaad.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
44 KB
19 KB
124ms
122ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/5583-26afedaf683dfaad.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
112c1d25efa2b678c451cf9e0934991a2c4ab33bda7362732035eca931d04c02

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
def5b722205ba3aa5dd5988f8d276a0d
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"b132-1a05f957328"
age
266788
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
XysmwiXj7KxrQYxVPo1Y1B2g4_MpTPHhPlb7rGkWNDtvwZiEYrJTbw==
date
Thu, 03 Sep 2026 17:09:03 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
3702-80b70e2415e5cfe4.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
38 KB
13 KB
126ms
123ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/3702-80b70e2415e5cfe4.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
0349939014cd852baeedd68b9086f11402fc092933a79b41200368fff7e25bc0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
0eb2b8c7a55807f0e96c8a0862b8f35f
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"981c-1a068706318"
age
253644
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
swZpAX0DDaTh-IbD2KXVf7k3APne7JPTnK38o1A-ykG9A0kfCqqBzw==
date
Thu, 03 Sep 2026 20:48:07 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 03 Sep 2026 18:03:11 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
page-f3c73f376ac71d7c.js Show response
login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/ Frame 4730
63 KB
24 KB
127ms
124ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/page-f3c73f376ac71d7c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
a4100ccc4ae5095360e141e05c6460939d445cb9342433d93d7cf1891cbfbab7

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
ce8f8bc2b0c33afe2aa30029eb91dfbb
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"fbc5-1a05f957328"
age
266787
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
dYoc6UNeZDGKB7kri1B-5d5RPCqZeRkRBwKOtXOq-yzHFOwvdRcAFA==
date
Thu, 03 Sep 2026 17:09:04 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
layout-b04bb2a093feb409.js Show response
login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/ Frame 4730
2 KB
2 KB
128ms
126ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/layout-b04bb2a093feb409.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
d5d29794308ac749280226a96ecc90ea3d792584102f375de5303e757eeccac8

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
54fbe2d0576c63aee1f14f1a5c04a9fb
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"965-1a05f957328"
age
266831
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
pizOJze-fqt76GcKucSFtS6aDgJBv4SH4xUWty49gUX1BpayctFHCw==
date
Thu, 03 Sep 2026 17:08:20 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
870fdd6f-8d99bcb08144c133.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
3 KB
2 KB
130ms
128ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/870fdd6f-8d99bcb08144c133.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
6edb3d79d78a71471a5cf2db8030726112f736d759d829960b4f09e28b9d2c9c

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
453fac226ef40df1cce446a8c1561e79
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"c8f-1a01fc3c5d8"
age
1473341
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
HjeDxLwVF6NwmZtF9LjbOxVFQzOCUFwNotROCwTN3_2TOs6h0Zl2jA==
date
Thu, 20 Aug 2026 17:59:50 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
1268-3b83b3e1626c34a3.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
67 KB
19 KB
132ms
131ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/1268-3b83b3e1626c34a3.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
931476948151549076352090726063fefe5bb2230ef1d25d7635234baa5f3d6e

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
0c9cb62adda702194be31ae0d49d7889
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"10aab-1a01fc3c5d8"
age
1473341
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
oiyNH2hMq-FAZVsexlrS0tpepS1ZTpVgRXFexd5E164_XJSMz8ZFdg==
date
Thu, 20 Aug 2026 17:59:50 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
5457-4404fbbe9faf3969.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
8 KB
3 KB
131ms
130ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/5457-4404fbbe9faf3969.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
fe9bd96e0ce46e7486fa752a8237bf9f6d67a73f025d93720f527c56c60c3a3f

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
24f469d761c2c263d1fbaeb79beacb0c
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"1f42-1a01fc3c5d8"
age
1473341
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
Oxa1i1oyebuXSqzD05kjqjqY73KfJiJ4WtU8RM1rYxxV_gAYmOmDUg==
date
Thu, 20 Aug 2026 17:59:50 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
7218-1d50492b1b34f3e4.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
22 KB
10 KB
131ms
130ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/7218-1d50492b1b34f3e4.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
ce742fde83df2e50e5ebd960fb46b116dcb3c31206803b1578dff98d3dee8af6

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
e2bd813baf05ff2d3650fe088acdc23f
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"58d6-1a05f957328"
age
266832
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
QQRnBEUR9K02sWnwZRSrgN0m9illhhE5jEx20xsJQIOxHnkeBZL7QQ==
date
Thu, 03 Sep 2026 17:08:19 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
page-9cbaa315eed2ff06.js Show response
login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/biometrics/error/ Frame 4730
22 KB
11 KB
133ms
132ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/biometrics/error/page-9cbaa315eed2ff06.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
b6494cef03556a679e18a4e5438cfff2d2c22648bc5254a751d12a70d6daa979

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
aaf69c149ea4365c88c6cf113948add0
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"59e4-1a05f957328"
age
266832
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
-EvXinzJomptkx2R1p87zFYyBw6VngKw2mRBh_a4XSnSX-M81iSthQ==
date
Thu, 03 Sep 2026 17:08:19 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
page-25ad13a984f54e58.js Show response
login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/account-picker/ Frame 4730
52 KB
22 KB
134ms
131ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/account-picker/page-25ad13a984f54e58.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
0b124069609a32bfb7f2ac5e4a9dbc2e916e416ddbd23925334bb977a9e5cf9d

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
6b3ee643e76b644920256edd22427d14
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"cec8-1a05f957328"
age
266805
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
vfiV-knhDYniRPsC7Uvq1cbr1nPw8UnZde599cx2pZmJ3JJTmb_qWQ==
date
Thu, 03 Sep 2026 17:08:46 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
9616-8d2ae84bac1918e1.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
9 KB
4 KB
132ms
130ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/9616-8d2ae84bac1918e1.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
99eff934922ee99762496335b5b3721b4a680e9a67cf050dba61142d7bb7972c

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
b37348205c774ae853f1fe0d90c4fa2b
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"2564-1a01fc3c5d8"
age
1473341
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
BPGpwSctZOf2Y9pnJPAoUbnBJN-jdbkjypC7Rivns0NHIT6moMWKag==
date
Thu, 20 Aug 2026 17:59:50 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
5872-9565f14e9b1965a5.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
17 KB
7 KB
133ms
132ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/5872-9565f14e9b1965a5.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
8c27be07effd21b4e71899ee37e132683c834acb73964d8fa2b080dd852e3b88

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
a6cb2ba77dcc8371129da6e7e96eb5cc
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"42ea-1a05f957328"
age
266787
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
uezGMmMrbb8ETkrxEsp13MFOngcNJexIRxwbLJnH5G6A2pUvA5FHww==
date
Thu, 03 Sep 2026 17:09:04 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
page-7201bacecd53c25b.js Show response
login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/consent/ Frame 4730
17 KB
7 KB
134ms
132ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/consent/page-7201bacecd53c25b.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
4d228290ab4c37fe1936d60e35aa833117d44ca4fea972346c8aa80080096f9f

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
37405407e94f8fcb56183e03d258aa16
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"4416-1a05f957328"
age
266787
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
nQ56VdKGvGBZfnc-btsz55SMtsX8sRuM-vPjDXly4-0SGtsvo_VfWw==
date
Thu, 03 Sep 2026 17:09:04 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
6425-dee44a4026d8722f.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
67 KB
18 KB
135ms
134ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/6425-dee44a4026d8722f.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
7b4f94d55963f642e0fd381df578b443f38132007428c5646c24f0fb50b054ca

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
1bead111ec6cd0aa7c3f70ca70ac776a
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"10b57-1a01fc3c5d8"
age
1473341
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
WAAIzaEHY80oPz7SrHj45UrKxEFSZ3EZHC4a5fsug-KNtKaQVe8Uwg==
date
Thu, 20 Aug 2026 17:59:50 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
6085-32c7d127e4921377.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
8 KB
4 KB
138ms
137ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/6085-32c7d127e4921377.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
0b8156e1b87d716f830065a3392cdd4156dff009f836c6d0fd1ebaacd3b0043d

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
0b9336699c3f57c247a203360f8974b2
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"20bc-1a05f957328"
age
266793
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
729vOvTyf0V1xMqXnoSB_ub-X4vxg5NswO8jcwRUCw23ETm9k6dOJw==
date
Thu, 03 Sep 2026 17:08:58 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
5607-8710bf06d063a065.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
28 KB
14 KB
137ms
136ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/5607-8710bf06d063a065.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
59b22d174346866f2c0787c4128d7818a5ec800113d71034f5ea19916786afe8

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
ebbb1bf0331ae891cb94dc6d80ac9b50
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"7143-1a05f957328"
age
266793
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
BLvV6CRiPuV6_Ye5YOIhJ1rUn2bQ72_svnPw1w0kWnZ1NaWgEWJBww==
date
Thu, 03 Sep 2026 17:08:58 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
page-ef41f5974bc9cfa2.js Show response
login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/device/ Frame 4730
11 KB
5 KB
160ms
159ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/device/page-ef41f5974bc9cfa2.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
e3e8aabd39e811dcfeb5bcb20addd60daa43a2eaae61e4159ea3a8b18d9a6b8a

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
26229f563714b7f6681f9b96da2f8ca4
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"2b7a-1a05f957328"
age
266832
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
7UvdTNjxHANOHyK6HRq_2Tbsy6A25n1cpMwmHGw2LaJBMVicU-A0Gg==
date
Thu, 03 Sep 2026 17:08:19 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
sync Show response
am-match.taboola.com/ Frame 7877
7 KB
7 KB
361ms
121ms
Document
text/html
141.226.228.48
TABOOLA-AS Tabool...
General
Full URL
https://am-match.taboola.com/sync?dast=V9kekCABYDAOCg-NNdmUJrBADgoPjTXZlCawUAAAAABgYAawcAJLRwuTymhcOt3GxGa9FuNlsLdxvLWrAaTpyDwWTiMk2GAEBCC5fLY1o43MrNZrQW7WaztXC3sawFq-HEORhMJi7TZAoAH8ZymQxqgYRl9vsOCsrp6TG7DKKi622xO5xmzxsA4tB0Onyue73C4vHNNX63X_D3nP6a0Vrt8NmdptfJ5VY5LKej4_XwutxCp-nz1ttND8vT79YcHV6n3eeWucymt-Zhd0tclrvDcnLa_W6N33U3Pd-qz8_z1jycn79iudstd4vJXg4AAAAAAA8A_____xAAAAAAABEAAAAAABIAAAAAABQAARUA_xYAAhcAAAAAABgA_____xoAAGcbAALUIAcAAr3MBoXtafsHAAAAAAAIAAAAAAAJAAAAAEAJAAAAAMAJwP________9_DMAAfeaNDMD_____DYBBDwDAgw8AwIMQAAAAQMgQwH8BxoD0hKYkEQCAwEhcEYAjgEkAnQBQAVhUAfz___dbAQBcAQAABIDilaxuZAHoDkq8hQEAAAAMjAEs0MPi95sddo3f7TKA_________38zgP8zgH80ACGAI9c0AKEFD1w1gF9AAIA1gF9AAAA2AHUD-P9_AwiAAwg7AAAAAIA7gP___389AJBbGBbD0cQ0MoxGi-XIOXPZTKaFZznYbYyjhXPhPYAcck6P7aJG8D6ACmuaXH6DpOUyGxQUv-1lkLFcJvsBTNhitJpMNsvhbLmYDIaj4Wi0P4CBWE0GCEDRksVqOVztJovRZrGYLHfD0WSCABQtGkxWo9FkMRmuRpPVbLnY7TYIQNGq1Wy0GQxXs8lst1sNB8PlaIQAE7YYrSaTzXI4Wy4mg-FoOBoNESCGFsuFx2TxrSWG5cotmngma4lhM1qrZhvPYuSamXyD1Vr0-pgei-VutFgttgggGHC4F8nTIp3INp6RxeIbOWYmw2YwW-yGy4nF5HKYhsvRxLjYWMQSzckincgu-97CsBiOJqaRYTRaLEfOmctmMi08y8FuYxwtnAt_abFceEwW31piWK7coolnspYYNqO1arbxLEaumck3WK1Fr4_psVjuRovVYt_YDYe7yWQxWe4bu-FwN5ksJst9h87wXX3ORmc1MvPo1FfZ8yPSOQwKl8HiXatOJ213eHCuDEanTP1UFnRGv9_v9_v9fr_f7zdoPQezQeE75xzG77j8knar5cfBYzAYHSaD0WE0GA2KWCK4SCcKi8dvuv1eFrfC4vGNHRaxRGm6SCd6wd9z-mtGa7XDZ3eaXieXW-WwnI6O18Prcgudps9bbzc9LE-_W3N0eJ12n1vmMpvemofdLXFZ7g7LyWn3uzV-1930fKs-P89b83B-_orlbrfcLSYTsURwukgnopfxdFG_EgAAAAAAAAAAwBLAJgAAAAAAJ0AALBcAQGL5WxcAGAQAAAAAAGAXIBoFS0e0tXDrGAAiLB6_6fZ7WdwKi8c3dlgZAEAiVpIZYDPAZwCCmNPZsgYAAAAQwAYAAAAo4wbYDcAbQIAaHAf4___3pwcAAABY2wcAYgo8cqXQC-cHKJjJajTYPwCAAIWY09nqdmNOZysgoCAGm9FgAgH_____BAEAAAAAAAB_HAgBAttuQgCFAIMhWv5ulxcCOgQA2AkqRnvCkz4EAAAEgOKVqHJBBFgQhUEhM-gXWqPxYDAYDAaVWVc0GBEQcJsIQLDVbrgbCFajCPj___-vCFhIBoUxGSsZFMZqFgEAdoKK0q9FLhcBAAABoHglqGgYAQ0x3M0Vq7liMpzLVtMIACjjCCAgFqdLjwA!&excid=22&docw=0&cijs=1&nlb=false
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.2, ECDHE_ECDSA, AES_128_GCM
Server
141.226.228.48 , Netherlands, ASN200478 (TABOOLA-AS Taboola.com ltd, IL),
Reverse DNS
Software
nginx /
Resource Hash
63ce395126170dc9dfe4b8da6948b1d0243c9cf60278a3164fec6dd7e11b8e6c

Request headers

Referer
https://abc7.com/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

content-type
text/html;charset=ISO-8859-1
date
Sun, 06 Sep 2026 19:15:31 GMT
machineid
440103
server
nginx
GET
H2
200
cmTagINSTREAM.js Show response
vidstat.taboola.com/vpaid/units/36_2_4/infra/
472 KB
95 KB
114ms
112ms
Script
application/javascript
151.101.1.44
Fastly
General
Full URL
https://vidstat.taboola.com/vpaid/units/36_2_4/infra/cmTagINSTREAM.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.1.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
AmazonS3-br /
Resource Hash
d4eed0f8a78bc09fcb07c6947604095837e2a17d9b66bd9e93e73dfc7d7c7176

Request headers

Origin
https://abc7.com
sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
etag
"1fc0087b04d8e65bb20d086603829f27"
age
732774
access-control-allow-methods
GET, OPTIONS, HEAD
x-cache
HIT
date
Sun, 06 Sep 2026 19:15:31 GMT
last-modified
Sat, 29 Aug 2026 07:41:38 GMT
vary
Accept-Encoding
x-served-by
cache-fra-eddf8230135-FRA
content-type
application/javascript
x-amz-id-2
0wfiCF4Tg+QBoY+SPyx57QJG08ENnhpcEUqLCeWhMDXTZHv7+wMt9xgGIk+HdoL5UBwLgRoLgzjIwhWqVOVU0uOGmNL5pAUP
x-cache-hits
46813
access-control-allow-headers
*
cache-control
public, max-age=2592000
x-timer
S1788722131.124356,VS0,VE0
via
1.1 varnish
x-amz-request-id
MVGR4D9HXW6GZ422
accept-ranges
bytes
access-control-allow-origin
*
content-length
97316
server
AmazonS3-br
x-amz-server-side-encryption
AES256
GET
H2
200
st
imprammp.taboola.com/
0
44 B
134ms
127ms
Image
text/plain
151.101.193.44
Fastly
General
Full URL
https://imprammp.taboola.com/st?cijs=convusmp&ttype=0&cisd=convusmp&cipid=66361655&crid=-1&dast=V9kekCABYDAOCg-NNdmUJrBADgoPjTXZlCawUAAAAABgYAawcAJLRwuTymhcOt3GxGa9FuNlsLdxvLWrAaTpyDwWTiMk2GAEBCC5fLY1o43MrNZrQW7WaztXC3sawFq-HEORhMJi7TZAoAH8ZymQxqgYRl9vsOCsrp6TG7DKKi622xO5xmzxsA4tB0Onyue73C4vHNNX63X_D3nP6a0Vrt8NmdptfJ5VY5LKej4_XwutxCp-nz1ttND8vT79YcHV6n3eeWucymt-Zhd0tclrvDcnLa_W6N33U3Pd-qz8_z1jycn79iudstd4vJXg4AAAAAAA8A_____xAAAAAAABEAAAAAABIAAAAAABQAARUA_xYAAhcAAAAAABgA_____xoAAGcbAALUIAcAAr3MBoXtafsHAAAAAAAIAAAAAAAJAAAAAEAJAAAAAMAJwP________9_DMAAfeaNDMD_____DYBBDwDAgw8AwIMQAAAAQMgQwH8BxoD0hKYkEQCAwEhcEYAjgEkAnQBQAVhUAfz___dbAQBcAQAABIDilaxuZAHoDkq8hQEAAAAMjAEs0MPi95sddo3f7TKA_________38zgP8zgH80ACGAI9c0AKEFD1w1gF9AAIA1gF9AAAA2AHUD-P9_AwiAAwg7AAAAAIA7gP___389AJBbGBbD0cQ0MoxGi-XIOXPZTKaFZznYbYyjhXPhPYAcck6P7aJG8D6ACmuaXH6DpOUyGxQUv-1lkLFcJvsBTNhitJpMNsvhbLmYDIaj4Wi0P4CBWE0GCEDRksVqOVztJovRZrGYLHfD0WSCABQtGkxWo9FkMRmuRpPVbLnY7TYIQNGq1Wy0GQxXs8lst1sNB8PlaIQAE7YYrSaTzXI4Wy4mg-FoOBoNESCGFsuFx2TxrSWG5cotmngma4lhM1qrZhvPYuSamXyD1Vr0-pgei-VutFgttgggGHC4F8nTIp3INp6RxeIbOWYmw2YwW-yGy4nF5HKYhsvRxLjYWMQSzckincgu-97CsBiOJqaRYTRaLEfOmctmMi08y8FuYxwtnAt_abFceEwW31piWK7coolnspYYNqO1arbxLEaumck3WK1Fr4_psVjuRovVYt_YDYe7yWQxWe4bu-FwN5ksJst9h87wXX3ORmc1MvPo1FfZ8yPSOQwKl8HiXatOJ213eHCuDEanTP1UFnRGv9_v9_v9fr_f7zdoPQezQeE75xzG77j8knar5cfBYzAYHSaD0WE0GA2KWCK4SCcKi8dvuv1eFrfC4vGNHRaxRGm6SCd6wd9z-mtGa7XDZ3eaXieXW-WwnI6O18Prcgudps9bbzc9LE-_W3N0eJ12n1vmMpvemofdLXFZ7g7LyWn3uzV-1930fKs-P89b83B-_orlbrfcLSYTsURwukgnopfxdFG_EgAAAAAAAAAAwBLAJgAAAAAAJ0AALBcAQGL5WxcAGAQAAAAAAGAXIBoFS0e0tXDrGAAiLB6_6fZ7WdwKi8c3dlgZAEAiVpIZYDPAZwCCmNPZsgYAAAAQwAYAAAAo4wbYDcAbQIAaHAf4___3pwcAAABY2wcAYgo8cqXQC-cHKJjJajTYPwCAAIWY09nqdmNOZysgoCAGm9FgAgH_____BAEAAAAAAAB_HAgBAttuQgCFAIMhWv5ulxcCOgQA2AkqRnvCkz4EAAAEgOKVqHJBBFgQhUEhM-gXWqPxYDAYDAaVWVc0GBEQcJsIQLDVbrgbCFajCPj___-vCFhIBoUxGSsZFMZqFgEAdoKK0q9FLhcBAAABoHglqGgYAQ0x3M0Vq7liMpzLVtMIACjjCCAgFqdLjwA!&cmcv=&pix=undefined&cb=1788722131057&uv=3624&tms=1788722131057&ft=0&unm=INSTREAM&aure=false&agl=101&cirid=4aeec4aa-9334-4766-87c2-058b9002be42&excid=e22lLINE_ITEM_ID_WILL_BE_HERE_ON_SERVINGc&tst=1&docw=0&cs=false
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-timer
S1788722131.131308,VS0,VE9
via
1.1 varnish
accept-ranges
bytes
x-cache
MISS
content-length
0
date
Sun, 06 Sep 2026 19:15:31 GMT
x-served-by
cache-lon4258-LON
server
nginx
x-cache-hits
0
GET
H2
200
st Show response
imprammp.taboola.com/ Frame 54D3
0
144 B
358ms
128ms
Document
text/plain
151.101.193.44
Fastly
General
Full URL
https://imprammp.taboola.com/st?cijs=convusmp&ttype=0&cisd=convusmp&cipid=66361655&crid=-1&dast=V9FjsCABYDAOCg-NNdmUJrBADgoPjTXZlCawUAAAAABgYA9AcAJDmYGEYT02qtm7hMa9FyM1tLfBPjWrOyuCzG3WZlswyGAECSg4lhNDGt1rqJy7QWLTeztcQ3Ma41K4vLYtxtVjbLYAoAH8ZymQxqgYRl9vsOCsrp6TG7DKKi622xO5xmzxsA4tB0Onyue73C4vHNNX63X_D3nP6a0Vrt8NmdptfJ5VY5LKej4_XwutxCp-nz1ttND8vT79YcHV6n3eeWucymt-Zhd0tclrvDcnLa_W6N33U3Pd-qz8_z1jycn79iudstd4vJXg4AAAAAAA8A_____xAAAAAAABEAAAAAABIAAAAAABQAARUA_xYAAhcAAAAAABgA_____xoAAGcbAALUIAcAAr3MBoXtafsHAAAAAAAIAAAAAAAJAEBB-UwJAAAIysUJwP________9_DMAAfeaNDMD_____DYBBDwDAgw8AwIMQAAAAQMgQAIQHmcpkA5wqEQCAwIhXEYAjgEkAnQBQAVhUAfz___dbAQBcAQAABIDilayCZAHoDkq8hQEAAAAMjAEs0MPi95sddo3f7TKA_________38zgP8zgH80ACGAI9c0AKEFD1w1gF9AAIA1gF9AAAA2AHUD-P9_AwiAAwg7AAAAAIA7gP___389AJBbGBbD0cQ0MoxGi-XIOXPZTKaFZznYbYyjhXPhPYAcck6P7aJG8D6AEGGZ_b6DgnJ6eswug6joelvsDqfZcxAfNAzLySCYH8CELUaryWSzHM6Wi8lgOBqORvsDGIjVZIAAFC1ZrJbD1W6yGG0Wi8lyNxxNJghA0aLBZDUaTRaT4Wo0Wc2Wi91ugwAUrVrNRpvBcDWbzHa71XAwXI5GCDBhi9FqMtksh7PlYjIYjoaj0RABYmixXHhMFt9aYliu3KKJZ7KWGDajtWq28SxGrpnJN1itRa-P6bFY7kaL1WKLAIIBh3uRPC3SiWzjGVksvpFjZjJsBrPFbricWEwuh2m4HE2Mi41FLNGcLNKJ7LLvLQyL4WhiGhlGo8Vy5Jy5bCbTwrMc7DbG0cK58JcWy4XHZPGtJYblyi2aeCZriWEzWqtmG89i5JqZfIPVWvT6mB6L5W60WC32jd1wuJtMFpPlvrEbDneTyWKy3HfoDN_V52x0ViMzj059lT0_Ip3DoHAZLN616nTSdocH58pgdMrUT2VBZ_T7_X6_3-_3-_1-g9ZzMBsUvnPOYfyOyy9pt1p-HDwGg9FhMhgdRoPRoIglgot0orB4_Kbb72VxKywe39hhEUuUpot0ohf8Pae_ZrRWO3x2p-l1crlVDsvp6Hg9vC630Gn6vPV208Py9Ls1R4fXafe5ZS6z6a152N0Sl-XusJycdr9b43fdTc-36vPzvDUP5-evWO52y91iMhFLBKeLdCJ6GU8X9SsBAAAAAAAAAAAsAWwCAAAAAHACGMxwtlmt1glwIIvBbrRYLRcAQGL5WxcAGAQAAAAAAGAXIBoFS0e0tXDrGAAiLB6_6fZ7WdwKi8c3dlgZAEAiVpIZYDPAZwCCmNPZsgYAAAAQwAYAAAAo4wbYDcAbQIAaHAf4___3pwcAAACg3wcAghJ75EKpH-YHKJjJajTYPwCAAIWY09nqdmNOZysgoCAGm9FgAgH_____BAEAAAAAAAB_HAgBAttuQgCFAIMhWv5ulxcCOgQA2AkqRnvCkz4EAAAEgOKVqHJBBFgQhUEhM-gXWqPxYDAYDAaVWVc0GBEQcJsIQLDVbrgbCFajCPj___-vCFhIBoUxGSsZFMZqFgEAdoKK0q9FKBcBAAABoHglqGgYAQ0x3M0Vq7liMpzLVtMIACjjCCAgFqdLjwA!&cmcv=&pix=undefined&cb=1788722131068&uv=3624&tms=1788722131068&abt=ufm&ft=0&unm=FEED_MANAGER&aure=false&agl=101&cirid=90b04b45-7be4-4936-b7b8-3ebeb873ef20&excid=e22lLINE_ITEM_ID_WILL_BE_HERE_ON_SERVINGc&tst=1&docw=0&cs=true&cias=1
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

Referer
https://abc7.com/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

accept-ranges
bytes
content-length
0
date
Sun, 06 Sep 2026 19:15:31 GMT
server
nginx
via
1.1 varnish
x-cache
MISS
x-cache-hits
0
x-served-by
cache-fra-eddf8230172-FRA
x-timer
S1788722131.360492,VS0,VE15
GET
H2
200
sync Show response
am-match.taboola.com/ Frame 5B9E
7 KB
7 KB
400ms
172ms
Document
text/html
141.226.228.48
TABOOLA-AS Tabool...
General
Full URL
https://am-match.taboola.com/sync?dast=V9FjsCABYDAOCg-NNdmUJrBADgoPjTXZlCawUAAAAABgYA9AcAJDmYGEYT02qtm7hMa9FyM1tLfBPjWrOyuCzG3WZlswyGAECSg4lhNDGt1rqJy7QWLTeztcQ3Ma41K4vLYtxtVjbLYAoAH8ZymQxqgYRl9vsOCsrp6TG7DKKi622xO5xmzxsA4tB0Onyue73C4vHNNX63X_D3nP6a0Vrt8NmdptfJ5VY5LKej4_XwutxCp-nz1ttND8vT79YcHV6n3eeWucymt-Zhd0tclrvDcnLa_W6N33U3Pd-qz8_z1jycn79iudstd4vJXg4AAAAAAA8A_____xAAAAAAABEAAAAAABIAAAAAABQAARUA_xYAAhcAAAAAABgA_____xoAAGcbAALUIAcAAr3MBoXtafsHAAAAAAAIAAAAAAAJAEBB-UwJAAAIysUJwP________9_DMAAfeaNDMD_____DYBBDwDAgw8AwIMQAAAAQMgQAIQHmcpkA5wqEQCAwIhXEYAjgEkAnQBQAVhUAfz___dbAQBcAQAABIDilayCZAHoDkq8hQEAAAAMjAEs0MPi95sddo3f7TKA_________38zgP8zgH80ACGAI9c0AKEFD1w1gF9AAIA1gF9AAAA2AHUD-P9_AwiAAwg7AAAAAIA7gP___389AJBbGBbD0cQ0MoxGi-XIOXPZTKaFZznYbYyjhXPhPYAcck6P7aJG8D6AEGGZ_b6DgnJ6eswug6joelvsDqfZcxAfNAzLySCYH8CELUaryWSzHM6Wi8lgOBqORvsDGIjVZIAAFC1ZrJbD1W6yGG0Wi8lyNxxNJghA0aLBZDUaTRaT4Wo0Wc2Wi91ugwAUrVrNRpvBcDWbzHa71XAwXI5GCDBhi9FqMtksh7PlYjIYjoaj0RABYmixXHhMFt9aYliu3KKJZ7KWGDajtWq28SxGrpnJN1itRa-P6bFY7kaL1WKLAIIBh3uRPC3SiWzjGVksvpFjZjJsBrPFbricWEwuh2m4HE2Mi41FLNGcLNKJ7LLvLQyL4WhiGhlGo8Vy5Jy5bCbTwrMc7DbG0cK58JcWy4XHZPGtJYblyi2aeCZriWEzWqtmG89i5JqZfIPVWvT6mB6L5W60WC32jd1wuJtMFpPlvrEbDneTyWKy3HfoDN_V52x0ViMzj059lT0_Ip3DoHAZLN616nTSdocH58pgdMrUT2VBZ_T7_X6_3-_3-_1-g9ZzMBsUvnPOYfyOyy9pt1p-HDwGg9FhMhgdRoPRoIglgot0orB4_Kbb72VxKywe39hhEUuUpot0ohf8Pae_ZrRWO3x2p-l1crlVDsvp6Hg9vC630Gn6vPV208Py9Ls1R4fXafe5ZS6z6a152N0Sl-XusJycdr9b43fdTc-36vPzvDUP5-evWO52y91iMhFLBKeLdCJ6GU8X9SsBAAAAAAAAAAAsAWwCAAAAAHACGMxwtlmt1glwIIvBbrRYLRcAQGL5WxcAGAQAAAAAAGAXIBoFS0e0tXDrGAAiLB6_6fZ7WdwKi8c3dlgZAEAiVpIZYDPAZwCCmNPZsgYAAAAQwAYAAAAo4wbYDcAbQIAaHAf4___3pwcAAACg3wcAghJ75EKpH-YHKJjJajTYPwCAAIWY09nqdmNOZysgoCAGm9FgAgH_____BAEAAAAAAAB_HAgBAttuQgCFAIMhWv5ulxcCOgQA2AkqRnvCkz4EAAAEgOKVqHJBBFgQhUEhM-gXWqPxYDAYDAaVWVc0GBEQcJsIQLDVbrgbCFajCPj___-vCFhIBoUxGSsZFMZqFgEAdoKK0q9FKBcBAAABoHglqGgYAQ0x3M0Vq7liMpzLVtMIACjjCCAgFqdLjwA!&excid=22&docw=0&cijs=1&nlb=false
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.2, ECDHE_ECDSA, AES_128_GCM
Server
141.226.228.48 , Netherlands, ASN200478 (TABOOLA-AS Taboola.com ltd, IL),
Reverse DNS
Software
nginx /
Resource Hash
b0436bbb5f02128cd7c43bb4c4cd168a4d526fcc376aba0398f4c4cbb6a5e25a

Request headers

Referer
https://abc7.com/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

content-type
text/html;charset=ISO-8859-1
date
Sun, 06 Sep 2026 19:15:31 GMT
machineid
440104
server
nginx
GET
H2
200
cmTagFEED_MANAGER.js Show response
vidstat.taboola.com/vpaid/units/36_2_4/infra/
614 KB
116 KB
174ms
174ms
Script
application/javascript
151.101.1.44
Fastly
General
Full URL
https://vidstat.taboola.com/vpaid/units/36_2_4/infra/cmTagFEED_MANAGER.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.1.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
AmazonS3-br /
Resource Hash
9aa831495e715b2909179080713409510ad1b1efcc6734afd8874c3f61444a62

Request headers

Origin
https://abc7.com
sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
etag
"4fd8ec6b44e80b782b4e2135aee13aab"
age
732779
access-control-allow-methods
GET, OPTIONS, HEAD
x-cache
HIT
date
Sun, 06 Sep 2026 19:15:31 GMT
last-modified
Sat, 29 Aug 2026 07:41:37 GMT
vary
Accept-Encoding
x-served-by
cache-fra-eddf8230135-FRA
content-type
application/javascript
x-amz-id-2
A3WNdl7svRC5Zbk2Tu+qQrKtbxkkAkQOrGa4/O8/rtoydZ7zjHFvjp8JKeAmGTaBRoxeH4C/cCw=
x-cache-hits
148882
access-control-allow-headers
*
cache-control
public, max-age=2592000
x-timer
S1788722131.135925,VS0,VE0
via
1.1 varnish
x-amz-request-id
7BCR0B07EBAEFF5B
accept-ranges
bytes
access-control-allow-origin
*
content-length
117964
server
AmazonS3-br
x-amz-server-side-encryption
AES256
GET
H2
200
s28785651495302
sw88.go.com/b/ss/wdgotvkabcresponsive,wdgotvsecondaryresponsive/1/JS-2.27.0/
43 B
189 B
115ms
115ms
Image
image/gif
63.140.62.210
Amazon.com
General
Full URL
https://sw88.go.com/b/ss/wdgotvkabcresponsive,wdgotvsecondaryresponsive/1/JS-2.27.0/s28785651495302?AQB=1&ndh=1&pf=1&t=6%2F8%2F2026%2022%3A15%3A30%200%20-180&mid=54109714201665181872321563256462948945&aamlh=6&ce=UTF-8&ns=abcotv&pageName=disasters-accidents%2Fpost_video%2F34magnitude-earthquake-hits-ontario-area-shaking-felt-across-san-bernardino-county-usgs-says%3D19779712&g=https%3A%2F%2Fabc7.com%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F&c.&module_name=no%20module%20title&page_name=disasters-accidents%2Fpost_video%2F34magnitude-earthquake-hits-ontario-area-shaking-felt-across-san-bernardino-county-usgs-says%3D19779712&page_url=https%3A%2F%2Fabc7.com%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F&story_title=3.4-magnitude%20earthquake%20hits%20Ontario%20area%2C%20shaking%20felt%20across%20San%20Bernardino%20County%2C%20USGS%20says&event_name=module%20impression&placement=right%20rail&creative_type=content&.c&server=kabc&pe=lnk_o&pev2=module%20impression&s=1600x1200&c=24&j=1.6&v=N&k=Y&bw=1600&bh=1200&mcorgid=19916ABB53224B2C0A490D45%40AdobeOrg&AQE=1
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
63.140.62.210 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ip-63-140-62-210.data.adobedc.net
Software
jag /
Resource Hash
a1ecbaed793a1f564c49c671f2dd0ce36f858534ef6d26b55783a06b884cc506
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
no-cache, no-store, max-age=0, no-transform, private
pragma
no-cache
etag
3841251528007352320-4613670000846066396
x-content-type-options
nosniff
expires
Sat, 05 Sep 2026 19:15:31 GMT
access-control-allow-origin
*
p3p
CP="This is not a P3P policy"
content-length
43
date
Sun, 06 Sep 2026 19:15:31 GMT
x-xss-protection
1; mode=block
last-modified
Mon, 07 Sep 2026 19:15:31 GMT
vary
*
server
jag
content-type
image/gif;charset=utf-8
GET
H2
200
id Show response
ident.mygaru.com/v2/
181 B
529 B
417ms
136ms
Fetch
application/json
192.145.111.2
mygaru_au Mygaru ...
General
Full URL
https://ident.mygaru.com/v2/id
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
192.145.111.2 , Ukraine, ASN207522 (mygaru_au Mygaru OU Private Limited Company, EE),
Reverse DNS
Software
/
Resource Hash
aca9f3161f61d150c95652f0663cc5112b5ee15e9396ae87cd3ba520b488c5b2

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

timing-allow-origin
*
content-encoding
gzip
access-control-allow-credentials
true
permissions-policy
browsing-topics=()
access-control-allow-origin
https://abc7.com
alt-svc
h3=":443"; ma=604800
content-length
180
date
Sun, 06 Sep 2026 19:15:30 GMT
content-type
application/json
vary
Accept-Encoding
GET
H/1.1
200
OK
pid Show response
sync6.im-apps.net/9001/
20 B
291 B
657ms
417ms
XHR
application/json
23.50.131.159
AKAMAI-ASN1 Akama...
General
Full URL
https://sync6.im-apps.net/9001/pid?ref=null&page=https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_256_GCM
Server
23.50.131.159 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a23-50-131-159.deploy.static.akamaitechnologies.com
Software
/
Resource Hash
3261d11727725d4d6b151e418e26751b5580e24787768c0ebd8a808e2a10a66c

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
Accept
application/json
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

Cache-Control
private, max-age=1800
Connection
keep-alive
Access-Control-Allow-Credentials
true
Access-Control-Allow-Origin
https://abc7.com
Content-Length
20
Date
Sun, 06 Sep 2026 19:15:31 GMT
Content-Type
application/json
Vary
Origin
GET
H2
204
increment Show response
id5-sync.com/api/esp/
0
224 B
349ms
113ms
XHR
text/plain
135.125.170.108
OVH OVH SAS
General
Full URL
https://id5-sync.com/api/esp/increment?counter=no-config
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
135.125.170.108 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
ns3270108.ip-135-125-170.eu
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=63072000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
Content-Type
text/plain
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=63072000; includeSubDomains; preload
access-control-allow-origin
https://abc7.com
date
Sun, 06 Sep 2026 19:15:31 GMT
vary
Origin, Access-Control-Request-Method, Access-Control-Request-Headers, Origin
access-control-allow-credentials
true
POST
H/1.1
202
Accepted
rum Show response
browser-intake-datadoghq.com/api/v2/ Frame 4730
53 B
464 B
681ms
263ms
Fetch
application/json
3.233.158.26
Amazon.com
General
Full URL
https://browser-intake-datadoghq.com/api/v2/rum?ddsource=browser&ddtags=sdk_version%3A5.31.1%2Capi%3Afetch%2Cenv%3Aprod%2Cservice%3Aidentity-ui%2Cversion%3A51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249&dd-api-key=pub3b1d5b26d9b77ebcdf2e8ba26cc9f858&dd-evp-origin-version=5.31.1&dd-evp-origin=browser&dd-request-id=89d2420d-c9c6-4f1e-92e1-56709e7d9176&dd-evp-encoding=deflate&batch_time=1788722131114
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/4170-dd4027ed6752dacf.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_128_GCM
Server
3.233.158.26 Ashburn, United States, ASN14618 (AMAZON-AES - Amazon.com, Inc., US),
Reverse DNS
ec2-3-233-158-26.compute-1.amazonaws.com
Software
/
Resource Hash
ff2e97cf3a552a458a7706f12e340373290f6192e38520706deb89a8c4497298
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
Content-Type
text/plain
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains; preload
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
access-control-allow-origin
*
content-length
53
accept-encoding
identity,gzip,x-gzip,deflate,x-deflate,zstd
date
Sun, 06 Sep 2026 19:15:31 GMT
content-type
application/json
dd-request-id
89d2420d-c9c6-4f1e-92e1-56709e7d9176
GET
H2
200
pd Show response
google-bidout-d.openx.net/w/1.0/ Frame 4B91
498 B
764 B
244ms
116ms
Document
text/html
35.244.159.8
Google LLC
General
Full URL
https://google-bidout-d.openx.net/w/1.0/pd?plm=5
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
35.244.159.8 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
8.159.244.35.bc.googleusercontent.com
Software
/
Resource Hash
f1ab9c13bada1d17a03f1123eec4c4d7206a009f7c65b2ea04db1f7b9ab246ab

Request headers

Referer
https://abc7.com/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cache-control
private, max-age=0, no-cache
content-encoding
br
content-length
375
content-type
text/html
date
Sun, 06 Sep 2026 19:15:30 GMT
p3p
CP="CUR ADM OUR NOR STA NID"
pragma
no-cache
vary
Accept, Accept-Encoding
via
1.1 google
x-forwarded-for
187.15.128.65
GET
H2
200
connect Show response
login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/device/ Frame 4730
6 KB
3 KB
109ms
107ms
Fetch
text/x-component
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/device/connect?_rsc=193yh
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/4170-dd4027ed6752dacf.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
3fd034486e3bac973fa90e8e1480af7073519cb7ca7fa9a97b53a1eb4a2b2372

Request headers

RSC
1
sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
Next-Router-State-Tree
%5B%22%22%2C%7B%22children%22%3A%5B%5B%22lang%22%2C%22en-US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22countryCode%22%2C%22US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22clientId%22%2C%22DATG-OTV.KABC.WEB%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%22v5%22%2C%7B%22children%22%3A%5B%22bridge%22%2C%7B%22children%22%3A%5B%22web%22%2C%7B%22children%22%3A%5B%22__PAGE__%22%2C%7B%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%2Ctrue%5D
Next-Url
/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
x-deployment-id
51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249

Response headers

x-request-id
d71012285a9cb67be5fa4a0a1d83c993
cache-control
public, s-maxage=900, max-age=0, must-revalidate, stale-while-revalidate=60, stale-if-error=900
content-encoding
gzip
age
672
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
UfzxyUygNMyfMowfORxw3geX4332FNCDNU7wHrY0P6FyExAEkAMefg==
date
Sun, 06 Sep 2026 19:04:19 GMT
content-type
text/x-component
vary
RSC,Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
dob-interstitial Show response
login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/ Frame 4730
6 KB
3 KB
109ms
107ms
Fetch
text/x-component
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/dob-interstitial?_rsc=193yh
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/4170-dd4027ed6752dacf.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
85f89d2837b4bd158e2ea83cd2856ac0dad9896150e5959ed30fb7b4d6fe5a97

Request headers

RSC
1
sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
Next-Router-State-Tree
%5B%22%22%2C%7B%22children%22%3A%5B%5B%22lang%22%2C%22en-US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22countryCode%22%2C%22US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22clientId%22%2C%22DATG-OTV.KABC.WEB%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%22v5%22%2C%7B%22children%22%3A%5B%22bridge%22%2C%7B%22children%22%3A%5B%22web%22%2C%7B%22children%22%3A%5B%22__PAGE__%22%2C%7B%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%2Ctrue%5D
Next-Url
/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
x-deployment-id
51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249

Response headers

x-request-id
0f329505c5f5411a139b288ec4d28b58
cache-control
public, s-maxage=900, max-age=0, must-revalidate, stale-while-revalidate=60, stale-if-error=900
content-encoding
gzip
age
672
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
ehmHoH7f_jb7etopvmuJCGsDSOBHrXnMCMnYbITM9bu8ouaqOg1Tcg==
date
Sun, 06 Sep 2026 19:04:19 GMT
content-type
text/x-component
vary
RSC,Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H3
200
JTUSjIg1_i6t8kCHKm459Wlhyw.woff2
fonts.gstatic.com/s/montserrat/v31/
37 KB
37 KB
236ms
115ms
Font
font/woff2
142.251.14.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/montserrat/v31/JTUSjIg1_i6t8kCHKm459Wlhyw.woff2
Requested by
Host: fonts.googleapis.com
URL: https://fonts.googleapis.com/css2?family=Montserrat:ital,wght@0,400;0,600&display=swap
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.14.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f94.1e100.net
Software
sffe /
Resource Hash
06b16db7a969135d48d38c49183be7fb88d4452e2a3011957c7851941f4e4879
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://abc7.com
sec-ch-ua-platform
"Linux"
Referer
https://fonts.googleapis.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

age
194638
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Sat, 04 Sep 2027 13:11:33 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 04 Sep 2026 13:11:33 GMT
last-modified
Thu, 04 Sep 2025 17:09:22 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
37956
x-xss-protection
0
server
sffe
GET
H3
200
JTUSjIg1_i6t8kCHKm459Wlhyw.woff2
fonts.gstatic.com/s/montserrat/v31/
37 KB
0
237ms
237ms
Font
font/woff2
142.251.14.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/montserrat/v31/JTUSjIg1_i6t8kCHKm459Wlhyw.woff2
Requested by
Host: fonts.googleapis.com
URL: https://fonts.googleapis.com/css2?family=Montserrat:ital,wght@0,400;0,600&display=swap
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.14.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f94.1e100.net
Software
sffe /
Resource Hash
06b16db7a969135d48d38c49183be7fb88d4452e2a3011957c7851941f4e4879
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://abc7.com
sec-ch-ua-platform
"Linux"
Referer
https://fonts.googleapis.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

age
194638
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Sat, 04 Sep 2027 13:11:33 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 04 Sep 2026 13:11:33 GMT
last-modified
Thu, 04 Sep 2025 17:09:22 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
37956
x-xss-protection
0
server
sffe
GET
H2
200
fed Show response
ups.analytics.yahoo.com/ups/58813/
2 B
248 B
437ms
168ms
XHR
application/json
87.248.119.251
YAHOO-DEB Yahoo-U...
General
Full URL
https://ups.analytics.yahoo.com/ups/58813/fed?gpp=DBABLA~BVQqAAAAAAJY.QA&gpp_sid=7&v=1&url=https%3A%2F%2Fabc7.com%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712%2F
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
87.248.119.251 , United Kingdom, ASN203220 (YAHOO-DEB Yahoo-UK Limited, GB),
Reverse DNS
e1-bmr.ycpi.vip.deb.yahoo.com
Software
ATS /
Resource Hash
44136fa355b3678a1146ad16f7e8649e94fb4fc21fe77e8310c060f61caaff8a
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
age
0
access-control-allow-credentials
true
x-content-type-options
nosniff
referrer-policy
no-referrer-when-downgrade
access-control-allow-origin
https://abc7.com
p3p
CP=NOI DSP COR LAW CURa DEVa TAIa PSAa PSDa OUR BUS UNI COM NAV
date
Sun, 06 Sep 2026 19:15:31 GMT
content-type
application/json
vary
Origin
server
ATS
GET
H2
200
error Show response
login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/ Frame 4730
5 KB
2 KB
107ms
107ms
Fetch
text/x-component
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/error?_rsc=193yh
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/4170-dd4027ed6752dacf.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
725aa1c9aa2dac15eac5254ca1baeaeafc1529eb5f75c5c105b6269a26f8b7ce

Request headers

RSC
1
sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
Next-Router-State-Tree
%5B%22%22%2C%7B%22children%22%3A%5B%5B%22lang%22%2C%22en-US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22countryCode%22%2C%22US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22clientId%22%2C%22DATG-OTV.KABC.WEB%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%22v5%22%2C%7B%22children%22%3A%5B%22bridge%22%2C%7B%22children%22%3A%5B%22web%22%2C%7B%22children%22%3A%5B%22__PAGE__%22%2C%7B%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%2Ctrue%5D
Next-Url
/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
x-deployment-id
51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249

Response headers

x-request-id
b0c1335189838e33129750c3c39b2a6e
cache-control
public, s-maxage=900, max-age=0, must-revalidate, stale-while-revalidate=60, stale-if-error=900
content-encoding
gzip
age
672
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
f5sHYe2yDjbgP_XuqD120yvzTAV5THRJuWCGmJIW7R4s6Y9DW16KdA==
date
Sun, 06 Sep 2026 19:04:19 GMT
content-type
text/x-component
vary
RSC,Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
galc Show response
login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/ Frame 4730
6 KB
3 KB
110ms
107ms
Fetch
text/x-component
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/galc?_rsc=193yh
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/4170-dd4027ed6752dacf.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
b2c42f8a1a4bd9265dc74c47e9abda151300a009170439fc711cbaabe5e4af78

Request headers

RSC
1
sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
Next-Router-State-Tree
%5B%22%22%2C%7B%22children%22%3A%5B%5B%22lang%22%2C%22en-US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22countryCode%22%2C%22US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22clientId%22%2C%22DATG-OTV.KABC.WEB%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%22v5%22%2C%7B%22children%22%3A%5B%22bridge%22%2C%7B%22children%22%3A%5B%22web%22%2C%7B%22children%22%3A%5B%22__PAGE__%22%2C%7B%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%2Ctrue%5D
Next-Url
/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
x-deployment-id
51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249

Response headers

x-request-id
1a1a594c65099562eb534fbd4c116a56
cache-control
public, s-maxage=900, max-age=0, must-revalidate, stale-while-revalidate=60, stale-if-error=900
content-encoding
gzip
age
666
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
YrLkgUFpsZeT3NadNRxIuh-fV46k4MLlINMrriVm-ktbvSwDVARRZA==
date
Sun, 06 Sep 2026 19:04:25 GMT
content-type
text/x-component
vary
RSC,Accept-Encoding
x-amz-cf-pop
FRA56-P10
POST
H2
204
bulk
trc.taboola.com/abcotvweb-abc7la/log/3/
0
489 B
281ms
274ms
Ping
image/gif
151.101.193.44
Fastly
General
Full URL
https://trc.taboola.com/abcotvweb-abc7la/log/3/bulk?route=AM%3AIL%3AV&lti=default&tvi48=32980&tvi50=32540&cv=20260906-3-RELEASE&bulkSize=9
Requested by
Host: cdn.taboola.com
URL: https://cdn.taboola.com/libtrc/abcotvweb-network/loader.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
Content-Type
application/x-www-form-urlencoded
sec-ch-ua-mobile
?0

Response headers

x-cache
MISS
p3p
policyref="http://trc.taboola.com/p3p.xml", CP="NOI DSP COR LAW NID CURa ADMa DEVa PSAa PSDa OUR BUS IND UNI COM NAV INT DEM"
date
Sun, 06 Sep 2026 19:15:31 GMT
content-type
image/gif
x-served-by
cache-lon4258-LON
x-cache-hits
0
cache-control
no-cache
x-fastly-to-nlb-rtt
71272
pragma
no-cache
x-timer
S1788722131.373034,VS0,VE100
x-vcl-time-ms
100
access-control-allow-credentials
true
via
1.1 varnish
accept-ranges
bytes
access-control-allow-origin
https://abc7.com
x-service-version
v1
server
nginx
GET
H2
200
id-flow Show response
login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/ Frame 4730
7 KB
3 KB
110ms
110ms
Fetch
text/x-component
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/id-flow?_rsc=193yh
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/4170-dd4027ed6752dacf.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
bff9914a93d0cd9a2e5b041910658feabe95256f18c4e2e8c995f86b51edc7ba

Request headers

RSC
1
sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
Next-Router-State-Tree
%5B%22%22%2C%7B%22children%22%3A%5B%5B%22lang%22%2C%22en-US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22countryCode%22%2C%22US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22clientId%22%2C%22DATG-OTV.KABC.WEB%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%22v5%22%2C%7B%22children%22%3A%5B%22bridge%22%2C%7B%22children%22%3A%5B%22web%22%2C%7B%22children%22%3A%5B%22__PAGE__%22%2C%7B%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%2Ctrue%5D
Next-Url
/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
x-deployment-id
51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249

Response headers

x-request-id
d1fd9c5e8963b078becfb86aed88733f
cache-control
public, s-maxage=900, max-age=0, must-revalidate, stale-while-revalidate=60, stale-if-error=900
content-encoding
gzip
age
43
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
7rr8PLAJBdJBrm_AJXZto3BCvnMkDTid9H24q2A7dcsS-CucW8fxfw==
date
Sun, 06 Sep 2026 19:14:48 GMT
content-type
text/x-component
vary
RSC,Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
f539211219b796ffbb49949997c764f0.png
cdn.taboola.com/libtrc/static/thumbnails/
254 B
760 B
118ms
117ms
Image
image/png
151.101.193.44
Fastly
General
Full URL
https://cdn.taboola.com/libtrc/static/thumbnails/f539211219b796ffbb49949997c764f0.png
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
AmazonS3 /
Resource Hash
f68019eb4b4e5933301d4ee75969e0cb94ed8333bf514630fa749eb9c3e483c9

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-fastly-object-storage
false
etag
"dfa7b52c86e56bd67fa4002f6ed19854"
x-amz-version-id
hL.cyLD7Q4TL5ceY.7JQwF9m5IYI8mkC
age
20960
x-cache
HIT
date
Sun, 06 Sep 2026 19:15:31 GMT
last-modified
Wed, 24 Jun 2015 07:14:11 GMT
x-served-by
cache-lon4258-LON
x-cache-hits
449
content-type
image/png
x-amz-id-2
mr354pKZVDR9hAvGsMuwcUZPDBiAfXiCMd5dOjPvaXzW3z2UC2YjhRsJUTJ3Q8JBikPKRCSG+yZyQ6WyBNYPk4USCmIMpDGn
x-amz-replication-status
COMPLETED
cache-control
private,max-age=31536000
x-amz-meta-s3cmd-attrs
uid:0/gname:root/uname:root/gid:0/mode:33188/mtime:1377415166/atime:1435052450/md5:dfa7b52c86e56bd67fa4002f6ed19854/ctime:1422381567
x-timer
S1788722131.312438,VS0,VE0
via
1.1 varnish
x-amz-request-id
4XMPXR4RAHXQVH1Q
accept-ranges
bytes
access-control-allow-origin
*
abp
15
content-length
254
server
AmazonS3
GET
H2
200
OvaMediaPlayer.js Show response
vidstat.taboola.com/vpaid/vPlayer/player/v18.1.9/
481 KB
88 KB
112ms
111ms
Script
application/javascript
151.101.1.44
Fastly
General
Full URL
https://vidstat.taboola.com/vpaid/vPlayer/player/v18.1.9/OvaMediaPlayer.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.1.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
AmazonS3-br /
Resource Hash
a2f1cff281f7cee60791934841096f247ec7f9b121208b5432a59f9e25be4b06

Request headers

Origin
https://abc7.com
sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
etag
"b3695918675be3ff1b0ad3de04396f73"
age
642789
access-control-allow-methods
GET, OPTIONS, HEAD
x-cache
HIT
date
Sun, 06 Sep 2026 19:15:31 GMT
last-modified
Sun, 30 Aug 2026 08:41:08 GMT
vary
Accept-Encoding
x-served-by
cache-fra-eddf8230135-FRA
content-type
application/javascript
x-amz-id-2
reUbUIOvf6QJApnftYD9YaBSeATPeuaDLM16uFYhKtQ/UFDpaWLiFDA0eyF/xls0Hkl1iI3io2jemrPwrzK6AF/KvYgDVQGh
x-cache-hits
149346
access-control-allow-headers
*
cache-control
public, max-age=2592000
x-timer
S1788722131.404271,VS0,VE0
via
1.1 varnish
x-amz-request-id
8RG041W68NTV6XSP
accept-ranges
bytes
access-control-allow-origin
*
content-length
89825
server
AmazonS3-br
x-amz-server-side-encryption
AES256
GET
H2
200
cmAdService.js
vidstat.taboola.com/vpaid/units/36_2_4/infra/
0
12 KB
124ms
123ms
Other
application/javascript
151.101.1.44
Fastly
General
Full URL
https://vidstat.taboola.com/vpaid/units/36_2_4/infra/cmAdService.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.1.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
AmazonS3 /
Resource Hash
1b76e60c57b71ae414a90cd7a4fd45cf10e1bf559420d4ef1f08e6dd9b40427d

Request headers

Origin
https://abc7.com
sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
Sec-Purpose
prefetch
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
"f82b0e72ca030761e5d58c4b9311405a"
age
732754
access-control-allow-methods
GET, OPTIONS, HEAD
x-cache
HIT
date
Sun, 06 Sep 2026 19:15:31 GMT
last-modified
Sat, 29 Aug 2026 07:41:28 GMT
x-served-by
cache-fra-eddf8230135-FRA
x-cache-hits
172010
content-type
application/javascript
x-amz-id-2
ed9t/Z03RjIKRHohkrxCNTc2x7anKlPX6V4MN3vkLzBnEREoehBrta5bNQjHG9DP616EpbjwzYY=
access-control-allow-headers
*
vary
Accept-Encoding
cache-control
public, max-age=2592000
x-timer
S1788722131.410572,VS0,VE0
via
1.1 varnish
x-amz-request-id
QC0549E8TNSC8TDD
accept-ranges
bytes
access-control-allow-origin
*
content-length
12238
server
AmazonS3
x-amz-server-side-encryption
AES256
POST
H2
204
pubs-generic
trc.taboola.com/abcotvweb-abc7la/log/3/
0
195 B
191ms
189ms
Ping
image/gif
151.101.193.44
Fastly
General
Full URL
https://trc.taboola.com/abcotvweb-abc7la/log/3/pubs-generic?route=AM%3AIL%3AV&lti=default&ri=cb4c4a2b1d43a3cb9336681455fcba9c&sd=v2_7a0184b4d04419d9fefd4a3907c84a9a_419acdb7-b09e-4b32-b034-56c31d5fd705-tuct11974151_1788722129_1788722129_CNawjgYQ35dLGNzUlsGHNCABKAEwZjiI6wpAsJAQSLzS2ANQ____________AVgAYABo9NCqw8yK475ycAGAAQCIAQCQAQA&ui=419acdb7-b09e-4b32-b034-56c31d5fd705-tuct11974151&pi=%2Fpost%2F34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says%2F19779712&wi=-3375350911853558437&pt=text&vi=1788722129500&tim=22%3A15%3A31.357&id=86519&llvl=2&cv=20260906-3-RELEASE&d=%7B%22data%22%3A%22%5C%22%5C%22%22%2C%22type%22%3A%22videoReel-visible_1_OC%22%7D
Requested by
Host: cdn.taboola.com
URL: https://cdn.taboola.com/libtrc/abcotvweb-network/loader.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
Content-Type
application/x-www-form-urlencoded
sec-ch-ua-mobile
?0

Response headers

x-cache
MISS
p3p
policyref="http://trc.taboola.com/p3p.xml", CP="NOI DSP COR LAW NID CURa ADMa DEVa PSAa PSDa OUR BUS IND UNI COM NAV INT DEM"
date
Sun, 06 Sep 2026 19:15:31 GMT
content-type
image/gif
x-served-by
cache-lon4258-LON
x-cache-hits
0
cache-control
no-cache
x-fastly-to-nlb-rtt
72151
pragma
no-cache
x-timer
S1788722131.418953,VS0,VE74
x-vcl-time-ms
74
access-control-allow-credentials
true
via
1.1 varnish
accept-ranges
bytes
access-control-allow-origin
https://abc7.com
x-service-version
v1
server
nginx
OPTIONS

wsg
27f19c7c68e3eadf7756fb7efdb661dd8909acf9.ipv4.cws.conviva.com/0/ Frame
0
0


OPTIONS

wsg
27f19c7c68e3eadf7756fb7efdb661dd8909acf9.ipv6.cws.conviva.com/0/ Frame
0
0


OPTIONS

wsg
27f19c7c68e3eadf7756fb7efdb661dd8909acf9.ipv4.cws.conviva.com/0/ Frame
0
0


OPTIONS

wsg
27f19c7c68e3eadf7756fb7efdb661dd8909acf9.ipv6.cws.conviva.com/0/ Frame
0
0


POST

wsg
27f19c7c68e3eadf7756fb7efdb661dd8909acf9.ipv4.cws.conviva.com/0/
0
0


POST

wsg
27f19c7c68e3eadf7756fb7efdb661dd8909acf9.ipv6.cws.conviva.com/0/
0
0


GET
H2
200
omid-session-client-v1.js Show response
hiveplayer-static.bamgrid.com/artifacts/hive/analytics/v2/
68 KB
14 KB
124ms
123ms
Script
application/javascript
99.84.152.107
Amazon.com
General
Full URL
https://hiveplayer-static.bamgrid.com/artifacts/hive/analytics/v2/omid-session-client-v1.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
99.84.152.107 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-99-84-152-107.fra56.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
a79b5d89711234608de96d76116093203cf780fe6c3754257ba9bfac3702eaaa

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-encoding
gzip
etag
W/"2fb1c41b37f294a803cde91ec9ad1dd7"
x-amz-version-id
0cR4BEkEBFdc82vDGdJQFkI8DdWWkC4S
age
8
via
1.1 2694fffaa67bb0ec65670b8dce8dcd24.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
V813RpFYCxjSRCn52sm5eHJbN8xeRw29sWvDxtKzyO7szzEsJSZ8kQ==
date
Sun, 06 Sep 2026 19:15:24 GMT
content-type
application/javascript
last-modified
Thu, 27 Mar 2025 17:19:28 GMT
server
AmazonS3
x-amz-cf-pop
FRA56-P13
x-amz-server-side-encryption
AES256
POST

wsg
27f19c7c68e3eadf7756fb7efdb661dd8909acf9.ipv4.cws.conviva.com/0/
0
0


POST

wsg
27f19c7c68e3eadf7756fb7efdb661dd8909acf9.ipv6.cws.conviva.com/0/
0
0


GET
H2
200
text-variable-full.woff2
display.asas.yango.tech/fonts/ Frame 595B
25 KB
26 KB
114ms
112ms
Font
font/woff2
212.102.56.178
CDN77 Datacamp Li...
General
Full URL
https://display.asas.yango.tech/fonts/text-variable-full.woff2
Requested by
Host: display.asas.yango.tech
URL: https://display.asas.yango.tech/ver/155/air_adaptive.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
212.102.56.178 Frankfurt am Main, Germany, ASN60068 (CDN77 Datacamp Limited, GB),
Reverse DNS
245149724.fra.cdn77.com
Software
CDN77-Turbo /
Resource Hash
033696b7f1ac04d1dcc102be84550e146236ceffc25a6cabc12aa51a6ee410b9
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff

Request headers

Origin
https://abc7.com
sec-ch-ua-platform
"Linux"
Referer
https://display.asas.yango.tech/ver/155/air_adaptive.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-amz-version-id
k4MU06SjrIdvlHN1FMW3Y5Wocr1KSPu3
etag
"7f0cdaf91230f9789ca4162aedff612e"
age
18134
x-77-cache
HIT
x-content-type-options
nosniff
x-amz-cf-id
bk2uLELuEq1ZiUQoSyVqSY54cBxyGQ_0BuzraXbjSgmyKyXTepQQew==
date
Sun, 06 Sep 2026 19:15:31 GMT
content-type
font/woff2
last-modified
Thu, 10 Jul 2025 13:33:15 GMT
x-77-nzt-ray
1cb09c0e3f52f8d3f8bb9d6af88aca24
strict-transport-security
max-age=31536000
x-77-nzt
kvIm5A7kcNhD5YXhadRI5/xaMV4g2lkK8VDufBDkRvBFNg+fojE5z4c
cache-control
public, max-age=31536000
via
1.1 db863971352ff4860373667d6300f00a.cloudfront.net (CloudFront)
accept-ranges
bytes
access-control-allow-origin
*
x-77-pop
frankfurtDE
content-length
26004
x-77-age
22565257
x-amz-cf-pop
FRA56-P13
server
CDN77-Turbo
x-amz-server-side-encryption
AES256
GET
H2
200
5269-15bc892c266078f6.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
6 KB
3 KB
109ms
108ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/5269-15bc892c266078f6.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
97dd8de6be42ad87fb361cee053b2c81e56d2783b3fc67547d4c23893ab65b27

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
970c02c232bc965bdd2fcf6ba9263f1e
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"1845-1a049b6dce0"
age
771907
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
xW4HDHQcPJVMExDk4A4XnvYD5vq8kWmYA2cMPcC-2-jBe4365IKF0Q==
date
Fri, 28 Aug 2026 20:50:24 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Fri, 28 Aug 2026 18:51:56 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
4427-e1f24d2b7f910958.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
8 KB
4 KB
109ms
109ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/4427-e1f24d2b7f910958.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
18cdf33581515c906aa6d2e42df60c0d12bce10e985e6bbdcd751944abd5653d

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
852a11a4979fd893d27e414bfd6b4ee7
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"1eb8-1a05f957328"
age
267124
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
BJRVcNGmLsq2NcMpR68Pi293fJL0MziZGlPr7Ko-NyjW3LQoqT3q9w==
date
Thu, 03 Sep 2026 17:03:27 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
page-a3bb4ccb530cc89d.js Show response
login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/device/connect/ Frame 4730
10 KB
5 KB
110ms
109ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/device/connect/page-a3bb4ccb530cc89d.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
0adcadd33559189ad8dabcdc06b014adc85703c806f753b1575d2e914f63c565

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
76378674ca2221319d013145555737ac
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"2642-1a05f957328"
age
266824
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
UlTuv-AjdPVr_xLgsBz7hUwsmZEWS-FPQsowrSBxzSBmHUDhmRS-Ew==
date
Thu, 03 Sep 2026 17:08:27 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
4330-2595b5231dca1756.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
78 KB
25 KB
111ms
110ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/4330-2595b5231dca1756.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
fdc4446a8f300a0982c9d9c71c7c5b4d49786b4d2c0472ea07ea80c571e295ef

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
51321dca06511e04002daab3e5b1d175
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"1394c-1a01fc3c5d8"
age
1473341
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
-Y84dAMgATU8qBLqcxkGiZGOYhixpuoz0lCs69iKmyrDg1eWLg8AMg==
date
Thu, 20 Aug 2026 17:59:50 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
8066-1d3ffcd83e285a6a.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
7 KB
4 KB
112ms
111ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/8066-1d3ffcd83e285a6a.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
e4407422d7283ac877bc992bd885bd5cd9a4014dfc101b38966061ac9f2a4131

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
c95acdca76cdd3624cf299f9978503a8
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"1cff-1a05f957328"
age
266805
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
i_R8b2AmBKfLPuMbj_1WIaDBBu3vcxSb8lM540rgi_JjaqPzagAPTg==
date
Thu, 03 Sep 2026 17:08:46 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
page-d39ac8c46e2e8a82.js Show response
login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/dob-interstitial/ Frame 4730
26 KB
12 KB
112ms
112ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/dob-interstitial/page-d39ac8c46e2e8a82.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
4c707488f4bc016e72dc1c6cc1c7a053e535585390d686e5878bfa254035f388

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
ab2e910f72163731aa1f85363c0d5dfb
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"671c-1a05f957328"
age
266805
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
fiABerNTIS2_JSR7VJNl1m-08_EtrcHHcmu_eYbI6yOpW9m6C5_d6w==
date
Thu, 03 Sep 2026 17:08:46 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
runner.html Show response
ep2.adtrafficquality.google/sodar/sodar2/255/ Frame F978
14 KB
6 KB
348ms
113ms
Document
text/html
142.251.14.132
Google LLC
General
Full URL
https://ep2.adtrafficquality.google/sodar/sodar2/255/runner.html
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.14.132 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f132.1e100.net
Software
sffe /
Resource Hash
c41f41da455986cf9d074c517db41020baf05e060802c11b45cb0a0a24f2a87e
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://abc7.com/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

accept-ranges
bytes
age
2277
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cache-control
public, max-age=3000
content-encoding
gzip
content-length
5457
content-type
text/html
cross-origin-opener-policy
same-origin; report-to="adspam-signals-scs"
cross-origin-resource-policy
cross-origin
date
Sun, 06 Sep 2026 18:37:34 GMT
expires
Sun, 06 Sep 2026 19:27:34 GMT
last-modified
Tue, 23 Jun 2026 02:06:19 GMT
report-to
{"group":"adspam-signals-scs","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/adspam-signals-scs"}]}
server
sffe
vary
Accept-Encoding
x-content-type-options
nosniff
x-xss-protection
0
GET
H3
200
aframe Show response
www.google.com/recaptcha/api2/ Frame 6174
829 B
566 B
122ms
122ms
Document
text/html
142.251.150.119
Google LLC
General
Full URL
https://www.google.com/recaptcha/api2/aframe
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.150.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
c2f483b30777983395d39e5b9ba671987f8d64c3db00b5bfa72f7ca38f63ca7a
Security Headers
Name Value
Content-Security-Policy script-src 'report-sample' 'nonce-kamcvgXU6pt2XOScmIegEQ' 'unsafe-inline' 'strict-dynamic' https: http: 'unsafe-eval';object-src 'none';base-uri 'self';report-uri https://csp.withgoogle.com/csp/recaptcha/1
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://abc7.com/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cache-control
private, max-age=300
content-encoding
gzip
content-security-policy
script-src 'report-sample' 'nonce-kamcvgXU6pt2XOScmIegEQ' 'unsafe-inline' 'strict-dynamic' https: http: 'unsafe-eval';object-src 'none';base-uri 'self';report-uri https://csp.withgoogle.com/csp/recaptcha/1
content-type
text/html; charset=utf-8
cross-origin-embedder-policy
require-corp
cross-origin-opener-policy-report-only
same-origin; report-to="coop_38fac9d5b82543fc4729580d18ff2d3d"
cross-origin-resource-policy
cross-origin
date
Sun, 06 Sep 2026 19:15:31 GMT
expires
Sun, 06 Sep 2026 19:15:31 GMT
report-to
{"group":"recaptcha","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/recaptcha"}]} {"group":"coop_38fac9d5b82543fc4729580d18ff2d3d","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/38fac9d5b82543fc4729580d18ff2d3d"}]}
server
ESF
x-content-type-options
nosniff
x-xss-protection
0
GET
H2
200
2205-038ef8a715537e62.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
48 KB
19 KB
111ms
110ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/2205-038ef8a715537e62.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
2ee7da7632babd7f6941c840e2d23133eaae146a02096fae399c43421db57aa0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
4d37462a2acfc222ab84922e8933d2f5
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"c01b-1a05f957328"
age
267039
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
1dZKaBWhIKbmpDZQaWkBBLryk-tkPYbw3S4hE8Jk9Ae3zWpmAW7jBg==
date
Thu, 03 Sep 2026 17:04:52 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
page-007c160043765e54.js Show response
login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/error/ Frame 4730
274 B
655 B
111ms
110ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/error/page-007c160043765e54.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
a49c44bc19a2497448f7f2a41111e188134a69c482681c72d28d66b04e087ba1

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
9af11e4337a9572584197f6882adecd3
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"112-1a049b6dce0"
age
771871
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
rCFYKs5cBHwiv4beBxMG1dkCQNSp_tQfblLzhUruSnIATXg12VdWLQ==
date
Fri, 28 Aug 2026 20:51:00 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Fri, 28 Aug 2026 18:51:56 GMT
vary
Accept-Encoding,Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
348-32862dbca58a369d.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
6 KB
3 KB
111ms
111ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/348-32862dbca58a369d.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
a73901f7eb14d4aa89a7f250c7eb9cba6126ea0d9395f545804cc253cb93c1b0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
345c33ca29efc8b799540a3a91c21e4a
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"18ce-1a01fc3c5d8"
age
1473341
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
QA0jHz7r3XaSnyK-1e5td51xqeB9We_D7GNSv7tZuG9WxYLSKoeMHA==
date
Thu, 20 Aug 2026 17:59:50 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
page-424ff84e424416be.js Show response
login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/galc/ Frame 4730
33 KB
16 KB
112ms
112ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/galc/page-424ff84e424416be.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
1575d56f863523fc877d485f116482ae1a25ca8a2dc4a42d695f73c3196835c5

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
ca4cb7d0ca58ab791e2c79670382e330
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"830f-1a05f957328"
age
266759
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
2CdgcXN8CfZSwRHFgmYRPIwIirRotvsMirz74_B9t2oIanRZiQhakA==
date
Thu, 03 Sep 2026 17:09:32 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
960-5609c857e772fac9.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
6 KB
3 KB
112ms
111ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/960-5609c857e772fac9.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
b86636d1d5496d749864661e7dae442aaa338219393bdc86d3835ff9df3ad763

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
faa0031083645a7ae5b7b83a1ea6ba5e
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"17d5-1a01fc3c5d8"
age
1473341
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
kZjDVSa29dO5iqBCMlUalPpodmv_8KORhqrBQ_NBPDrCEtzko5DdFg==
date
Thu, 20 Aug 2026 17:59:50 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
794-bfaa39a987b8ef8e.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
20 KB
8 KB
112ms
112ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/794-bfaa39a987b8ef8e.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
45fee736cbbba35cdb9f6b11efe8857463ee009a84abe9dfa8f159e7c1b97f59

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
b0cfedb710c627d2058d6bad151a1bbf
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"5061-1a05f957328"
age
266782
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
tbDAwFu9ylNFFjRf2zDI7D1Tfq4JuIHDM6pIhIW4A2ImdlFehrrHew==
date
Thu, 03 Sep 2026 17:09:09 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
page-fee721d3bd371d6e.js Show response
login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/id-flow/ Frame 4730
60 KB
25 KB
113ms
113ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/id-flow/page-fee721d3bd371d6e.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
e603f93d433b946a041bfd534cdf65cd8b5be6a339b4bc740cd6f4617f82ceb6

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
8e6fc37c27ab3325e8451490700bea15
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"f066-1a05f957328"
age
267004
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
rgjSJorFaoyk8qsQxBGJOjDUp4I-Dnh9g65zVnzTSM_HVS0H4vq5SA==
date
Thu, 03 Sep 2026 17:05:27 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
sd
us-u.openx.net/w/1.0/ Frame 4B91
Redirect Chain
  • https://cm.g.doubleclick.net/pixel?google_nid=openx&google_cm&google_sc
  • https://us-u.openx.net/w/1.0/sd?id=537072991&val=CAESEPNwFXcWM5XCcV-Nc7mMgpo&google_cver=1
43 B
136 B
124ms
119ms
Image
image/gif
35.244.159.8
Google LLC
General
Full URL
https://us-u.openx.net/w/1.0/sd?id=537072991&val=CAESEPNwFXcWM5XCcV-Nc7mMgpo&google_cver=1
Requested by
Host: google-bidout-d.openx.net
URL: https://google-bidout-d.openx.net/w/1.0/pd?plm=5
Protocol
H2
Server
35.244.159.8 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
8.159.244.35.bc.googleusercontent.com
Software
/
Resource Hash
4e0705327480ad2323cb03d9c450ffcae4a98bf3a5382fa0c7882145ed620e49

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
Referer
https://google-bidout-d.openx.net/

Response headers

cache-control
private, max-age=0, no-cache
pragma
no-cache
x-forwarded-for
187.15.128.65
via
1.1 google
expires
Mon, 26 Jul 1997 05:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
43
p3p
CP="CUR ADM OUR NOR STA NID"
date
Sun, 06 Sep 2026 19:15:31 GMT
content-type
image/gif
vary
Accept

Redirect headers

cache-control
no-cache, must-revalidate
location
https://us-u.openx.net/w/1.0/sd?id=537072991&val=CAESEPNwFXcWM5XCcV-Nc7mMgpo&google_cver=1
pragma
no-cache
cross-origin-resource-policy
cross-origin
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
content-length
295
date
Sun, 06 Sep 2026 19:15:31 GMT
x-xss-protection
0
content-type
text/html; charset=UTF-8
server
HTTP server (unknown)
GET
H3
200
pixel
cm.g.doubleclick.net/ Frame 4B91
170 B
188 B
127ms
126ms
Image
image/png
142.251.13.157
Google LLC
General
Full URL
https://cm.g.doubleclick.net/pixel?google_nid=openx&google_hm=OWVkYjU0OGYtZmE4NS0yYWM4LWRlMzAtMmVhYmQ4MTQzNGZk
Requested by
Host: google-bidout-d.openx.net
URL: https://google-bidout-d.openx.net/w/1.0/pd?plm=5
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.13.157 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
wt-in-f157.1e100.net
Software
HTTP server (unknown) /
Resource Hash
0b8a20373c6dd04e091902226d922b3688143a8938afb9d283d889de7b55ceb5
Security Headers
Name Value
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://google-bidout-d.openx.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, must-revalidate
pragma
no-cache
cross-origin-resource-policy
cross-origin
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
170
date
Sun, 06 Sep 2026 19:15:31 GMT
x-xss-protection
0
content-type
image/png
server
HTTP server (unknown)
GET
H2
200
sd
us-u.openx.net/w/1.0/ Frame 4B91
Redirect Chain
  • https://match.adsrvr.org/track/cmf/openx?oxid=b2b48745-33f2-746c-cbd0-741212f6fa9d&gdpr=0
  • https://match.adsrvr.org/track/cmb/openx?oxid=b2b48745-33f2-746c-cbd0-741212f6fa9d&gdpr=0
  • https://us-u.openx.net/w/1.0/sd?id=537072971&val=854f06c6-0e88-4afd-a936-6a879ff410f4&ttd_puid=b2b48745-33f2-746c-cbd0-741212f6fa9d&gdpr=0&gdpr_consent=
43 B
97 B
119ms
118ms
Image
image/gif
35.244.159.8
Google LLC
General
Full URL
https://us-u.openx.net/w/1.0/sd?id=537072971&val=854f06c6-0e88-4afd-a936-6a879ff410f4&ttd_puid=b2b48745-33f2-746c-cbd0-741212f6fa9d&gdpr=0&gdpr_consent=
Requested by
Host: google-bidout-d.openx.net
URL: https://google-bidout-d.openx.net/w/1.0/pd?plm=5
Protocol
H2
Server
35.244.159.8 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
8.159.244.35.bc.googleusercontent.com
Software
/
Resource Hash
4e0705327480ad2323cb03d9c450ffcae4a98bf3a5382fa0c7882145ed620e49

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
Referer
https://google-bidout-d.openx.net/

Response headers

cache-control
private, max-age=0, no-cache
pragma
no-cache
x-forwarded-for
187.15.128.65
via
1.1 google
expires
Mon, 26 Jul 1997 05:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
43
p3p
CP="CUR ADM OUR NOR STA NID"
date
Sun, 06 Sep 2026 19:15:32 GMT
content-type
image/gif
vary
Accept

Redirect headers

location
https://us-u.openx.net/w/1.0/sd?id=537072971&val=854f06c6-0e88-4afd-a936-6a879ff410f4&ttd_puid=b2b48745-33f2-746c-cbd0-741212f6fa9d&gdpr=0&gdpr_consent=
content-length
335
date
Sun, 06 Sep 2026 19:15:32 GMT
server
Kestrel
GET
H2
200
sd
us-u.openx.net/w/1.0/ Frame 4B91
Redirect Chain
  • https://creativecdn.com/cm-notify?pi=openx&gdpr=0
  • https://creativecdn.com/cm-notify?pi=openx&gdpr=0&tc=1
  • https://us-u.openx.net/w/1.0/sd?id=537073053&val=rhvrGoZzJvZi2sQgRiU87MebV0cruRe4rSwCGZyXCtY&pi=openx&gdpr=0&tc=1
43 B
97 B
119ms
117ms
Image
image/gif
35.244.159.8
Google LLC
General
Full URL
https://us-u.openx.net/w/1.0/sd?id=537073053&val=rhvrGoZzJvZi2sQgRiU87MebV0cruRe4rSwCGZyXCtY&pi=openx&gdpr=0&tc=1
Requested by
Host: google-bidout-d.openx.net
URL: https://google-bidout-d.openx.net/w/1.0/pd?plm=5
Protocol
H2
Server
35.244.159.8 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
8.159.244.35.bc.googleusercontent.com
Software
/
Resource Hash
4e0705327480ad2323cb03d9c450ffcae4a98bf3a5382fa0c7882145ed620e49

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
Referer
https://google-bidout-d.openx.net/

Response headers

cache-control
private, max-age=0, no-cache
pragma
no-cache
x-forwarded-for
187.15.128.65
via
1.1 google
expires
Mon, 26 Jul 1997 05:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
43
p3p
CP="CUR ADM OUR NOR STA NID"
date
Sun, 06 Sep 2026 19:15:32 GMT
content-type
image/gif
vary
Accept

Redirect headers

expires
Thu, 01 Jan 1970 00:00:00 GMT
cache-control
no-cache, no-store, must-revalidate, private, max-age=0
location
https://us-u.openx.net/w/1.0/sd?id=537073053&val=rhvrGoZzJvZi2sQgRiU87MebV0cruRe4rSwCGZyXCtY&pi=openx&gdpr=0&tc=1
content-length
0
date
Sun, 06 Sep 2026 19:15:32 GMT
pragma
no-cache
vary
Accept-Encoding
GET
H2
200
sd
eu-u.openx.net/w/1.0/ Frame 4B91
Redirect Chain
  • https://c1.adform.net/serving/cookie/match?party=22
  • https://c1.adform.net/serving/cookie/match?CC=1&party=22
  • https://eu-u.openx.net/w/1.0/sd?id=537113484&val=4965478313182929533
43 B
97 B
122ms
116ms
Image
image/gif
35.244.159.8
Google LLC
General
Full URL
https://eu-u.openx.net/w/1.0/sd?id=537113484&val=4965478313182929533
Requested by
Host: google-bidout-d.openx.net
URL: https://google-bidout-d.openx.net/w/1.0/pd?plm=5
Protocol
H2
Server
35.244.159.8 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
8.159.244.35.bc.googleusercontent.com
Software
/
Resource Hash
4e0705327480ad2323cb03d9c450ffcae4a98bf3a5382fa0c7882145ed620e49

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
Referer
https://google-bidout-d.openx.net/

Response headers

cache-control
private, max-age=0, no-cache
pragma
no-cache
x-forwarded-for
187.15.128.65
via
1.1 google
expires
Mon, 26 Jul 1997 05:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
43
p3p
CP="CUR ADM OUR NOR STA NID"
date
Sun, 06 Sep 2026 19:15:32 GMT
content-type
image/gif
vary
Accept

Redirect headers

strict-transport-security
max-age=31536000; includeSubDomains
access-control-max-age
86400
cache-control
no-cache, no-store, must-revalidate, no-transform
location
https://eu-u.openx.net/w/1.0/sd?id=537113484&val=4965478313182929533
pragma
no-cache
accept-ch
Sec-CH-UA,Sec-CH-UA-Arch,Sec-CH-UA-Bitness,Sec-CH-UA-Full-Version-List,Sec-CH-UA-Mobile,Sec-CH-UA-Model,Sec-CH-UA-Platform,Sec-CH-UA-Platform-Version
access-control-allow-credentials
true
access-control-allow-methods
GET
expires
-1
access-control-allow-origin
*
content-length
0
date
Sun, 06 Sep 2026 19:15:32 GMT
server
nginx
access-control-allow-headers
Content-Type,Cache-Control,Accept-Encoding,X-Requested-With
GET
H3
204
gen_204
pagead2.googlesyndication.com/pagead/ Frame 595B
0
0
234ms
233ms
Fetch
image/gif
142.251.127.157
Google LLC
General
Full URL
https://pagead2.googlesyndication.com/pagead/gen_204?id=av-js&type=fle-fetch-start2
Requested by
Host: pagead2.googlesyndication.com
URL: https://pagead2.googlesyndication.com/pagead/managed/js/activeview/current/ufs_web_display.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.127.157 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfrai-in-f157.1e100.net
Software
cafe /
Resource Hash
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
0
date
Sun, 06 Sep 2026 19:15:31 GMT
x-xss-protection
0
content-type
image/gif
server
cafe
GET
H3
204
gen_204
pagead2.googlesyndication.com/pagead/ Frame 595B
0
0
229ms
228ms
Fetch
image/gif
142.251.127.157
Google LLC
General
Full URL
https://pagead2.googlesyndication.com/pagead/gen_204?id=av-js&type=colleague-executed&name=4
Requested by
Host: pagead2.googlesyndication.com
URL: https://pagead2.googlesyndication.com/pagead/managed/js/activeview/current/ufs_web_display.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.127.157 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfrai-in-f157.1e100.net
Software
cafe /
Resource Hash
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
0
date
Sun, 06 Sep 2026 19:15:31 GMT
x-xss-protection
0
content-type
image/gif
server
cafe
GET
DATA
200
OK
truncated
/ Frame 595B
213 B
0
Image
image/png

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
5c5623d078172cb55ef52f37561c58037355157b3671268842c66a0e97c6f9d9

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/png
GET
H2
200
huge
avatars.asas.yango.tech/get-air/15055020/2a0000019fc940bd09e169f4c822183bde8c/ Frame 595B
18 KB
19 KB
348ms
110ms
Image
image/webp
195.181.170.18
CDN77 Datacamp Li...
General
Full URL
https://avatars.asas.yango.tech/get-air/15055020/2a0000019fc940bd09e169f4c822183bde8c/huge
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
195.181.170.18 Frankfurt am Main, Germany, ASN60068 (CDN77 Datacamp Limited, GB),
Reverse DNS
610407756.fra.cdn77.com
Software
CDN77-Turbo /
Resource Hash
21cb6973b3d3d88c4beb606de455e7f898ba7b9fb45313c62307c222b8567c25

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
419224989e367830
age
1265420
x-77-cache
HIT
x-amz-cf-id
Fn-rkHcFzu_iZJloFM3PtzZHUNSgYmv91azyzLU_6njWFSd6rXwQ9w==
date
Sun, 06 Sep 2026 19:15:32 GMT
content-type
image/webp
last-modified
Mon, 03 Aug 2026 22:35:24 GMT
x-77-nzt-ray
4c1562245f00e984f9bb9d6a4349fa05
x-77-nzt
kts5WiH4kjs5ObhUgCx768xJItnk3jGF2w3HpguTDluCVWmKQAoqGq4
cache-control
max-age=31536000,immutable
timing-allow-origin
*
access-control-allow-credentials
true
via
1.1 18df62d606ad91f0ecd51963c7b7d50a.cloudfront.net (CloudFront)
accept-ranges
bytes
access-control-allow-origin
*
x-77-pop
frankfurtDE
content-length
18512
x-77-age
1660156
x-amz-cf-pop
FRA56-P14
server
CDN77-Turbo
GET
H2
200
simmons.co.il
favicon.asas.yango.tech/favicon/ Frame 595B
898 B
1 KB
357ms
113ms
Image
image/png
79.127.216.203
CDN77 Datacamp Li...
General
Full URL
https://favicon.asas.yango.tech/favicon/simmons.co.il?size=32&stub=2
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
79.127.216.203 Frankfurt am Main, Germany, ASN60068 (CDN77 Datacamp Limited, GB),
Reverse DNS
651293913.fra.cdn77.com
Software
CDN77-Turbo /
Resource Hash
c9a9ac96101376e94d1b12da35c6905f916efd7b52659e131fabae03f284b24c
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

age
22
x-77-cache
HIT
x-content-type-options
nosniff
x-amz-cf-id
i3kKHXolqUKSP3zWoF8h6vkfgpeD5f0G5lQ8u9dc7xv1moLfAziRHw==
date
Sun, 06 Sep 2026 19:15:32 GMT
content-type
image/png
x-77-nzt-ray
d9f4d126d2c626dbf9bb9d6af0874706
x-77-nzt
kmq/a66luQoSMFkAPPCSBtwMRk6/siPG4LCMopua0JTTdK1z9psaimI
cache-control
max-age=43200
via
1.1 9d6dcca9f87a0cfb0dd2e9c599881c68.cloudfront.net (CloudFront)
accept-ranges
bytes
access-control-allow-origin
*
x-77-pop
frankfurtDE
content-length
898
x-xss-protection
1; mode=block
x-77-age
19091
x-amz-cf-pop
FRA56-P16
server
CDN77-Turbo
GET
H3
200
reach_worklet.html Show response
www.googleadservices.com/pagead/managed/js/activeview/current/ Frame 90E5
93 B
93 B
125ms
125ms
Document
text/html
142.251.13.157
Google LLC
General
Full URL
https://www.googleadservices.com/pagead/managed/js/activeview/current/reach_worklet.html
Requested by
Host: scripts.webcontentassessor.com
URL: https://scripts.webcontentassessor.com/scripts/fea4ac1291b1ab4b9e08331b030dbfca29ba761aae7f184704ffd867755688c0
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.13.157 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
wt-in-f157.1e100.net
Software
cafe /
Resource Hash
136b3dfa7c254f92a9a3513c191c87c05f7c7ff7f82c6d648a33496c3c380593
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://abc7.com/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cache-control
private, max-age=3600, stale-while-revalidate=3600
content-encoding
br
content-length
69
content-type
text/html; charset=UTF-8
cross-origin-resource-policy
cross-origin
date
Sun, 06 Sep 2026 19:15:31 GMT
etag
9658810392779322030
expires
Sun, 06 Sep 2026 19:15:31 GMT
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
server
cafe
timing-allow-origin
*
vary
Accept-Encoding
x-content-type-options
nosniff
x-xss-protection
0
GET

0a022017-dea7-4e7e-96c3-9c29218fae02
https://abc7.com/
0
0


GET
H2
200
TBPrebidHookHandler.js Show response
vidstat.taboola.com/vpaid/vPlayer/player/v18.1.9/
10 KB
4 KB
115ms
114ms
Script
application/javascript
151.101.1.44
Fastly
General
Full URL
https://vidstat.taboola.com/vpaid/vPlayer/player/v18.1.9/TBPrebidHookHandler.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.1.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
AmazonS3 /
Resource Hash
ec890851d67d305f2fcca4e7af233b7deac337d96f11bf497694abdcecc4d4ab

Request headers

Origin
https://abc7.com
sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
"9d4de9ec21538421bf4a7a402c58248f"
age
641940
access-control-allow-methods
GET, OPTIONS, HEAD
x-cache
HIT
date
Sun, 06 Sep 2026 19:15:31 GMT
last-modified
Sun, 30 Aug 2026 08:40:59 GMT
x-served-by
cache-fra-eddf8230135-FRA
x-cache-hits
44948
content-type
application/javascript
x-amz-id-2
TUgo7VjALGQWCpHAvV54gJPmPAxDZbw3AT+DWVyMEcExBMs+bOQN5kExWFeYoR/enBeX9jXJanPCjwo96ykizopmMsQzG24u
access-control-allow-headers
*
vary
Accept-Encoding
cache-control
public, max-age=2592000
x-timer
S1788722132.900803,VS0,VE0
via
1.1 varnish
x-amz-request-id
NDBG2GTEFWHGM2T3
accept-ranges
bytes
access-control-allow-origin
*
content-length
3842
server
AmazonS3
x-amz-server-side-encryption
AES256
GET

40951b4c-f6da-4f3e-9525-33098f965f9e
https://abc7.com/
0
0


POST
H/1.1
200
OK
cors Show response
data.ad-score.com/data/
43 B
582 B
976ms
497ms
Fetch
text/plain
130.211.115.4
Google LLC
General
Full URL
https://data.ad-score.com/data/cors?pm_st=ZAgpvRMGLHTSnapkpESgWYuUKlAvvrhd-FE7fPshldVrrKD8b2nLOG0/HPg==-E03JNMpnaFrhMw==&pm_ct=94d34ee3e9872c5833d8beab&pm_pl=1788722131866&pm_td=12&pid=1000075&en=1.1&callback=__pm_glbl_Y6LZTTypw0HzblvYECBCcKEp._gc1&tt=g&v=7cf6c29
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_128_GCM
Server
130.211.115.4 Council Bluffs, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
4.115.211.130.bc.googleusercontent.com
Software
/
Resource Hash
645f5bce0c8bb2f814b025b9db305324f2ef8091a5f9487532f3693c4d2770be

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
Content-Type
text/plain
sec-ch-ua-mobile
?0

Response headers

Cache-Control
post-check=0, pre-check=0, false, proxy-revalidate, no-cache, no-cache=Set-Cookie, no-store, must-revalidate, max-age=0, s-maxage=0
Pragma
no-cache
Age
0
Connection
keep-alive
Access-Control-Allow-Credentials
true
Access-Control-Allow-Methods
POST
Access-Control-Allow-Origin
https://abc7.com
P3p
CP="CURa ADMa DEVa TAIi PSAi PSDi IVAi IVDi CONi HISa TELi OUR IND DSP CAO COR"
Content-Length
43
Date
Sun, 06 Sep 2026 19:15:32 GMT
Content-Type
text/plain; charset=utf-8
POST
H2
204
debug
il-trc-events.taboola.com/abcotvweb-abc7la/log/2/
0
123 B
113ms
113ms
Ping
text/plain
185.106.33.48
TABOOLA-AS Tabool...
General
Full URL
https://il-trc-events.taboola.com/abcotvweb-abc7la/log/2/debug?type=warn&msg=protected%20media%3A%20onFraudScriptLoaded&lt=default&tvi48=32980&tvi50=32540&tim=22%3A15%3A31.924&id=42300&cv=20260906-3-RELEASE&llvl=2
Requested by
Host: cdn.taboola.com
URL: https://cdn.taboola.com/libtrc/abcotvweb-network/loader.js
Protocol
H2
Security
TLS 1.2, ECDHE_ECDSA, AES_128_GCM
Server
185.106.33.48 , Israel, ASN200478 (TABOOLA-AS Taboola.com ltd, IL),
Reverse DNS
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
Content-Type
application/x-www-form-urlencoded
sec-ch-ua-mobile
?0

Response headers

access-control-allow-origin
https://abc7.com
x-fastly-to-nlb-rtt
55519
date
Sun, 06 Sep 2026 19:15:31 GMT
server
nginx
access-control-allow-credentials
true
GET
H3
200
anchor Show response
www.google.com/recaptcha/enterprise/ Frame 3444
53 KB
28 KB
143ms
143ms
Document
text/html
142.251.150.119
Google LLC
General
Full URL
https://www.google.com/recaptcha/enterprise/anchor?ar=1&k=6LcnzusZAAAAABiX7zUG2lN9BBH_1ERH1pfyR95-&co=aHR0cHM6Ly9sb2dpbi5kaXNuZXkuY29tOjQ0Mw..&hl=iw&v=8x-4t2pegToiW8KmThtO4AQt&size=invisible&anchor-ms=20000&execute-ms=30000&cb=72ilyxa5gdw7
Requested by
Host: www.gstatic.com
URL: https://www.gstatic.com/recaptcha/releases/8x-4t2pegToiW8KmThtO4AQt/recaptcha__iw.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.150.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
fe8635935ade4e9659d0a70bf145621974ab148b852bff8aabd73816fddb2a8e
Security Headers
Name Value
Content-Security-Policy script-src 'report-sample' 'nonce--j6cNgO8GFat5HVxat88DQ' 'unsafe-inline' 'strict-dynamic' https: http: 'unsafe-eval';object-src 'none';base-uri 'self';report-uri https://csp.withgoogle.com/csp/recaptcha/1
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://login.disney.com/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cache-control
no-cache, no-store, max-age=0, must-revalidate
content-encoding
gzip
content-security-policy
script-src 'report-sample' 'nonce--j6cNgO8GFat5HVxat88DQ' 'unsafe-inline' 'strict-dynamic' https: http: 'unsafe-eval';object-src 'none';base-uri 'self';report-uri https://csp.withgoogle.com/csp/recaptcha/1
content-type
text/html; charset=utf-8
cross-origin-embedder-policy
require-corp
cross-origin-opener-policy-report-only
same-origin; report-to="coop_38fac9d5b82543fc4729580d18ff2d3d"
cross-origin-resource-policy
cross-origin
date
Sun, 06 Sep 2026 19:15:32 GMT
expires
Mon, 01 Jan 1990 00:00:00 GMT
pragma
no-cache
report-to
{"group":"recaptcha","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/recaptcha"}]} {"group":"coop_38fac9d5b82543fc4729580d18ff2d3d","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/38fac9d5b82543fc4729580d18ff2d3d"}]}
server
ESF
x-content-type-options
nosniff
x-xss-protection
0
GET
H2
200
usync.html Show response
eus.rubiconproject.com/ Frame B2F1
269 B
380 B
397ms
112ms
Document
text/html
23.219.139.145
Akamai Technologies
General
Full URL
https://eus.rubiconproject.com/usync.html?p=16698&endpoint=us-east&gdpr=0&us_privacy=1NN-
Requested by
Host: am-match.taboola.com
URL: https://am-match.taboola.com/sync?dast=V9kekCABYDAOCg-NNdmUJrBADgoPjTXZlCawUAAAAABgYAawcAJLRwuTymhcOt3GxGa9FuNlsLdxvLWrAaTpyDwWTiMk2GAEBCC5fLY1o43MrNZrQW7WaztXC3sawFq-HEORhMJi7TZAoAH8ZymQxqgYRl9vsOCsrp6TG7DKKi622xO5xmzxsA4tB0Onyue73C4vHNNX63X_D3nP6a0Vrt8NmdptfJ5VY5LKej4_XwutxCp-nz1ttND8vT79YcHV6n3eeWucymt-Zhd0tclrvDcnLa_W6N33U3Pd-qz8_z1jycn79iudstd4vJXg4AAAAAAA8A_____xAAAAAAABEAAAAAABIAAAAAABQAARUA_xYAAhcAAAAAABgA_____xoAAGcbAALUIAcAAr3MBoXtafsHAAAAAAAIAAAAAAAJAAAAAEAJAAAAAMAJwP________9_DMAAfeaNDMD_____DYBBDwDAgw8AwIMQAAAAQMgQwH8BxoD0hKYkEQCAwEhcEYAjgEkAnQBQAVhUAfz___dbAQBcAQAABIDilaxuZAHoDkq8hQEAAAAMjAEs0MPi95sddo3f7TKA_________38zgP8zgH80ACGAI9c0AKEFD1w1gF9AAIA1gF9AAAA2AHUD-P9_AwiAAwg7AAAAAIA7gP___389AJBbGBbD0cQ0MoxGi-XIOXPZTKaFZznYbYyjhXPhPYAcck6P7aJG8D6ACmuaXH6DpOUyGxQUv-1lkLFcJvsBTNhitJpMNsvhbLmYDIaj4Wi0P4CBWE0GCEDRksVqOVztJovRZrGYLHfD0WSCABQtGkxWo9FkMRmuRpPVbLnY7TYIQNGq1Wy0GQxXs8lst1sNB8PlaIQAE7YYrSaTzXI4Wy4mg-FoOBoNESCGFsuFx2TxrSWG5cotmngma4lhM1qrZhvPYuSamXyD1Vr0-pgei-VutFgttgggGHC4F8nTIp3INp6RxeIbOWYmw2YwW-yGy4nF5HKYhsvRxLjYWMQSzckincgu-97CsBiOJqaRYTRaLEfOmctmMi08y8FuYxwtnAt_abFceEwW31piWK7coolnspYYNqO1arbxLEaumck3WK1Fr4_psVjuRovVYt_YDYe7yWQxWe4bu-FwN5ksJst9h87wXX3ORmc1MvPo1FfZ8yPSOQwKl8HiXatOJ213eHCuDEanTP1UFnRGv9_v9_v9fr_f7zdoPQezQeE75xzG77j8knar5cfBYzAYHSaD0WE0GA2KWCK4SCcKi8dvuv1eFrfC4vGNHRaxRGm6SCd6wd9z-mtGa7XDZ3eaXieXW-WwnI6O18Prcgudps9bbzc9LE-_W3N0eJ12n1vmMpvemofdLXFZ7g7LyWn3uzV-1930fKs-P89b83B-_orlbrfcLSYTsURwukgnopfxdFG_EgAAAAAAAAAAwBLAJgAAAAAAJ0AALBcAQGL5WxcAGAQAAAAAAGAXIBoFS0e0tXDrGAAiLB6_6fZ7WdwKi8c3dlgZAEAiVpIZYDPAZwCCmNPZsgYAAAAQwAYAAAAo4wbYDcAbQIAaHAf4___3pwcAAABY2wcAYgo8cqXQC-cHKJjJajTYPwCAAIWY09nqdmNOZysgoCAGm9FgAgH_____BAEAAAAAAAB_HAgBAttuQgCFAIMhWv5ulxcCOgQA2AkqRnvCkz4EAAAEgOKVqHJBBFgQhUEhM-gXWqPxYDAYDAaVWVc0GBEQcJsIQLDVbrgbCFajCPj___-vCFhIBoUxGSsZFMZqFgEAdoKK0q9FLhcBAAABoHglqGgYAQ0x3M0Vq7liMpzLVtMIACjjCCAgFqdLjwA!&excid=22&docw=0&cijs=1&nlb=false
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
23.219.139.145 Frankfurt am Main, Germany, ASN16625 (AKAMAI-AS - Akamai Technologies, Inc., US),
Reverse DNS
a23-219-139-145.deploy.static.akamaitechnologies.com
Software
Apache/2.4.65 (Debian) /
Resource Hash
e4df52d49c57bc3e7158cb052cc05c60f1258c24de5c5728dac5d43272943ad9

Request headers

Referer
https://am-match.taboola.com/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

accept-ranges
bytes
content-encoding
gzip
content-length
224
content-type
text/html
date
Sun, 06 Sep 2026 19:15:32 GMT
etag
"10d-64e67a048fd80-gzip"
last-modified
Wed, 01 Apr 2026 15:20:38 GMT
server
Apache/2.4.65 (Debian)
vary
Accept-Encoding
GET
H2
200
usermatch Show response
ssum.casalemedia.com/ Frame B9F8
Redirect Chain
  • https://ssum.casalemedia.com/usermatch?gdpr=0&s=183756&us_privacy=1NN-&cb=https%3A%2F%2Fsync.taboola.com%2Fsg%2Fcasale-network%2F1%2Frtb-h%2F%3Ftaboola_hm%3D%5Bpartner_user_id%5D%26orig%3Dvideo%26u...
  • https://ssum.casalemedia.com/usermatch?cb=https%3A%2F%2Fsync.taboola.com%2Fsg%2Fcasale-network%2F1%2Frtb-h%2F%3Ftaboola_hm%3D%5Bpartner_user_id%5D%26orig%3Dvideo%26us_privacy%3D1NN-&gdpr=0&s=183756...
2 KB
885 B
292ms
291ms
Document
text/html
104.18.27.193
Cloudflare
General
Full URL
https://ssum.casalemedia.com/usermatch?cb=https%3A%2F%2Fsync.taboola.com%2Fsg%2Fcasale-network%2F1%2Frtb-h%2F%3Ftaboola_hm%3D%5Bpartner_user_id%5D%26orig%3Dvideo%26us_privacy%3D1NN-&gdpr=0&s=183756&us_privacy=1NN-&C=1
Requested by
Host: am-match.taboola.com
URL: https://am-match.taboola.com/sync?dast=V9kekCABYDAOCg-NNdmUJrBADgoPjTXZlCawUAAAAABgYAawcAJLRwuTymhcOt3GxGa9FuNlsLdxvLWrAaTpyDwWTiMk2GAEBCC5fLY1o43MrNZrQW7WaztXC3sawFq-HEORhMJi7TZAoAH8ZymQxqgYRl9vsOCsrp6TG7DKKi622xO5xmzxsA4tB0Onyue73C4vHNNX63X_D3nP6a0Vrt8NmdptfJ5VY5LKej4_XwutxCp-nz1ttND8vT79YcHV6n3eeWucymt-Zhd0tclrvDcnLa_W6N33U3Pd-qz8_z1jycn79iudstd4vJXg4AAAAAAA8A_____xAAAAAAABEAAAAAABIAAAAAABQAARUA_xYAAhcAAAAAABgA_____xoAAGcbAALUIAcAAr3MBoXtafsHAAAAAAAIAAAAAAAJAAAAAEAJAAAAAMAJwP________9_DMAAfeaNDMD_____DYBBDwDAgw8AwIMQAAAAQMgQwH8BxoD0hKYkEQCAwEhcEYAjgEkAnQBQAVhUAfz___dbAQBcAQAABIDilaxuZAHoDkq8hQEAAAAMjAEs0MPi95sddo3f7TKA_________38zgP8zgH80ACGAI9c0AKEFD1w1gF9AAIA1gF9AAAA2AHUD-P9_AwiAAwg7AAAAAIA7gP___389AJBbGBbD0cQ0MoxGi-XIOXPZTKaFZznYbYyjhXPhPYAcck6P7aJG8D6ACmuaXH6DpOUyGxQUv-1lkLFcJvsBTNhitJpMNsvhbLmYDIaj4Wi0P4CBWE0GCEDRksVqOVztJovRZrGYLHfD0WSCABQtGkxWo9FkMRmuRpPVbLnY7TYIQNGq1Wy0GQxXs8lst1sNB8PlaIQAE7YYrSaTzXI4Wy4mg-FoOBoNESCGFsuFx2TxrSWG5cotmngma4lhM1qrZhvPYuSamXyD1Vr0-pgei-VutFgttgggGHC4F8nTIp3INp6RxeIbOWYmw2YwW-yGy4nF5HKYhsvRxLjYWMQSzckincgu-97CsBiOJqaRYTRaLEfOmctmMi08y8FuYxwtnAt_abFceEwW31piWK7coolnspYYNqO1arbxLEaumck3WK1Fr4_psVjuRovVYt_YDYe7yWQxWe4bu-FwN5ksJst9h87wXX3ORmc1MvPo1FfZ8yPSOQwKl8HiXatOJ213eHCuDEanTP1UFnRGv9_v9_v9fr_f7zdoPQezQeE75xzG77j8knar5cfBYzAYHSaD0WE0GA2KWCK4SCcKi8dvuv1eFrfC4vGNHRaxRGm6SCd6wd9z-mtGa7XDZ3eaXieXW-WwnI6O18Prcgudps9bbzc9LE-_W3N0eJ12n1vmMpvemofdLXFZ7g7LyWn3uzV-1930fKs-P89b83B-_orlbrfcLSYTsURwukgnopfxdFG_EgAAAAAAAAAAwBLAJgAAAAAAJ0AALBcAQGL5WxcAGAQAAAAAAGAXIBoFS0e0tXDrGAAiLB6_6fZ7WdwKi8c3dlgZAEAiVpIZYDPAZwCCmNPZsgYAAAAQwAYAAAAo4wbYDcAbQIAaHAf4___3pwcAAABY2wcAYgo8cqXQC-cHKJjJajTYPwCAAIWY09nqdmNOZysgoCAGm9FgAgH_____BAEAAAAAAAB_HAgBAttuQgCFAIMhWv5ulxcCOgQA2AkqRnvCkz4EAAAEgOKVqHJBBFgQhUEhM-gXWqPxYDAYDAaVWVc0GBEQcJsIQLDVbrgbCFajCPj___-vCFhIBoUxGSsZFMZqFgEAdoKK0q9FLhcBAAABoHglqGgYAQ0x3M0Vq7liMpzLVtMIACjjCCAgFqdLjwA!&excid=22&docw=0&cijs=1&nlb=false
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.18.27.193 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
1b07758a6c914480fe6799b58cba533a2be2054469672bd4fd369ed7f7c8936b

Request headers

Referer
https://am-match.taboola.com/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

alt-svc
h3=":443"; ma=86400
cache-control
no-cache
cf-cache-status
DYNAMIC
cf-ray
a36fcd90bbebd22e-FRA
content-encoding
br
content-type
text/html
date
Sun, 06 Sep 2026 19:15:32 GMT
expires
0
nel
{"report_to":"cf-nel","success_fraction":0.01,"max_age":604800}
p3p
policyref="/w3c/p3p.xml", CP="NOI DSP COR DEVa TAIa OUR BUS UNI"
pragma
no-cache
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=3lU9a5RZyRKa5NVpJKQqme5GhRsexbkNFQ15d3mrrNqONzWfVA84X5Iztxf5rQpjtJQl%2FxoVL4rp3CJWLGSAQJRjIwaae5AyFeBPAYD%2BMFQuNwF4Ac%2FXT7P00RswT90472fMmMNP"}]}
server
cloudflare

Redirect headers

alt-svc
h3=":443"; ma=86400
cache-control
no-cache
cf-cache-status
DYNAMIC
cf-ray
a36fcd8eedf8d22e-FRA
content-length
0
date
Sun, 06 Sep 2026 19:15:32 GMT
expires
0
location
/usermatch?cb=https%3A%2F%2Fsync.taboola.com%2Fsg%2Fcasale-network%2F1%2Frtb-h%2F%3Ftaboola_hm%3D%5Bpartner_user_id%5D%26orig%3Dvideo%26us_privacy%3D1NN-&gdpr=0&s=183756&us_privacy=1NN-&C=1
nel
{"report_to":"cf-nel","success_fraction":0.01,"max_age":604800}
p3p
policyref="/w3c/p3p.xml", CP="NOI DSP COR DEVa TAIa OUR BUS UNI"
pragma
no-cache
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=wWpZOuudcsULBCWs%2FHUYImjEuAyaDzyPL%2FPeF1QEjWBUKHiNB7sm5Co0FQzMsslOpR4Nl71twXdVRTi3Or02mTY1ZzWt8x3dit4Ntb4DBRFXFD%2F6joROYa%2BtKuoV2jR3snRibVS4"}]}
server
cloudflare
GET
H2
200
/
trc.taboola.com/sg/thetradedesk-network/1/rtb-h/ Frame 7877
Redirect Chain
  • https://match.adsrvr.org/track/cmf/generic?gdpr=0&ttd_pid=054f32o&us_privacy=1NN-&ttd_tpi=1
  • https://match.adsrvr.org/track/cmb/generic?gdpr=0&ttd_pid=054f32o&us_privacy=1NN-&ttd_tpi=1
  • https://trc.taboola.com/sg/thetradedesk-network/1/rtb-h/?taboola_hm=854f06c6-0e88-4afd-a936-6a879ff410f4
0
394 B
174ms
173ms
Image
text/plain
151.101.193.44
Fastly
General
Full URL
https://trc.taboola.com/sg/thetradedesk-network/1/rtb-h/?taboola_hm=854f06c6-0e88-4afd-a936-6a879ff410f4
Protocol
H2
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
Referer
https://am-match.taboola.com/

Response headers

x-fastly-to-nlb-rtt
59305
x-timer
S1788722132.317342,VS0,VE61
x-vcl-time-ms
61
via
1.1 varnish
accept-ranges
bytes
x-cache
MISS
content-length
0
date
Sun, 06 Sep 2026 19:15:32 GMT
x-service-version
v1
server
nginx
x-cache-hits
0
x-served-by
cache-fra-eddf8230172-FRA

Redirect headers

location
https://trc.taboola.com/sg/thetradedesk-network/1/rtb-h/?taboola_hm=854f06c6-0e88-4afd-a936-6a879ff410f4
content-length
239
date
Sun, 06 Sep 2026 19:15:32 GMT
server
Kestrel
GET
H2
200
omweb-v1.js Show response
hiveplayer-static.bamgrid.com/artifacts/hive/analytics/v2/
45 KB
16 KB
123ms
123ms
Script
application/javascript
99.84.152.107
Amazon.com
General
Full URL
https://hiveplayer-static.bamgrid.com/artifacts/hive/analytics/v2/omweb-v1.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
99.84.152.107 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-99-84-152-107.fra56.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
68ba160cf22e00ece6c9fa4792e964da488ba9ed0bb95bd2f3794599cd03c4e8

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-encoding
gzip
etag
W/"f402c68f48236b3ef5c34af6f3ddf93f"
x-amz-version-id
wIfNRAC_sMBmCcRZbCa6fCnPKNQIxosO
age
8
via
1.1 2694fffaa67bb0ec65670b8dce8dcd24.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
p2FcYkQkLksoD3XC3p3td-BLaQsb4KsNYISVIzNk_AeIk3Sb63csMw==
date
Sun, 06 Sep 2026 19:15:24 GMT
content-type
application/javascript
last-modified
Thu, 27 Mar 2025 17:19:52 GMT
server
AmazonS3
x-amz-cf-pop
FRA56-P13
x-amz-server-side-encryption
AES256
POST
H2
200
VideoBidRequestHandlerServlet Show response
wf.taboola.com/
20 KB
7 KB
481ms
472ms
XHR
application/json
151.101.193.44
Fastly
General
Full URL
https://wf.taboola.com/VideoBidRequestHandlerServlet?oid=15&width=718&height=481&pubid=165757&tagid=946347&crid=-1&noaop=12&sortOrderType=0&cb=1788722131994&mimes=5,10,11,12&isvideo=0&plmd=2&mindur=1&maxdur=210&minbr=1&maxbr=10000&st=0&seq=1&pv=1819&pt=0&tz=180&viewable=true&ddast=V9kekCABYDAOCg-NNdmUJrBADgoPjTXZlCawUAAAAABgYAawcAJLRwuTymhcOt3GxGa9FuNlsLdxvLWrAaTpyDwWTiMk2GAEBCC5fLY1o43MrNZrQW7WaztXC3sawFq-HEORhMJi7TZAoAH8ZymQxqgYRl9vsOCsrp6TG7DKKi622xO5xmzxsA4tB0Onyue73C4vHNNX63X_D3nP6a0Vrt8NmdptfJ5VY5LKej4_XwutxCp-nz1ttND8vT79YcHV6n3eeWucymt-Zhd0tclrvDcnLa_W6N33U3Pd-qz8_z1jycn79iudstd4vJXg4AAAAAAA8A_____xAAAAAAABEAAAAAABIAAAAAABQAARUA_xYAAhcAAAAAABgA_____xoAAGcbAALUIAcAAr3MBoXtafsHAAAAAAAIAAAAAAAJAAAAAEAJAAAAAMAJwP________9_DMAAfeaNDMD_____DYBBDwDAgw8AwIMQAAAAQMgQwH8BxoD0hKYkEQCAwEhcEYAjgEkAnQBQAVhUAfz___dbAQBcAQAABIDilaxuZAHoDkq8hQEAAAAMjAEs0MPi95sddo3f7TKA_________38zgP8zgH80ACGAI9c0AKEFD1w1gF9AAIA1gF9AAAA2AHUD-P9_AwiAAwg7AAAAAIA7gP___389AJBbGBbD0cQ0MoxGi-XIOXPZTKaFZznYbYyjhXPhPYAcck6P7aJG8D6ACmuaXH6DpOUyGxQUv-1lkLFcJvsBTNhitJpMNsvhbLmYDIaj4Wi0P4CBWE0GCEDRksVqOVztJovRZrGYLHfD0WSCABQtGkxWo9FkMRmuRpPVbLnY7TYIQNGq1Wy0GQxXs8lst1sNB8PlaIQAE7YYrSaTzXI4Wy4mg-FoOBoNESCGFsuFx2TxrSWG5cotmngma4lhM1qrZhvPYuSamXyD1Vr0-pgei-VutFgttgggGHC4F8nTIp3INp6RxeIbOWYmw2YwW-yGy4nF5HKYhsvRxLjYWMQSzckincgu-97CsBiOJqaRYTRaLEfOmctmMi08y8FuYxwtnAt_abFceEwW31piWK7coolnspYYNqO1arbxLEaumck3WK1Fr4_psVjuRovVYt_YDYe7yWQxWe4bu-FwN5ksJst9h87wXX3ORmc1MvPo1FfZ8yPSOQwKl8HiXatOJ213eHCuDEanTP1UFnRGv9_v9_v9fr_f7zdoPQezQeE75xzG77j8knar5cfBYzAYHSaD0WE0GA2KWCK4SCcKi8dvuv1eFrfC4vGNHRaxRGm6SCd6wd9z-mtGa7XDZ3eaXieXW-WwnI6O18Prcgudps9bbzc9LE-_W3N0eJ12n1vmMpvemofdLXFZ7g7LyWn3uzV-1930fKs-P89b83B-_orlbrfcLSYTsURwukgnopfxdFG_EgAAAAAAAAAAwBLAJgAAAAAAJ0AALBcAQGL5WxcAGAQAAAAAAGAXIBoFS0e0tXDrGAAiLB6_6fZ7WdwKi8c3dlgZAEAiVpIZYDPAZwCCmNPZsgYAAAAQwAYAAAAo4wbYDcAbQIAaHAf4___3pwcAAABY2wcAYgo8cqXQC-cHKJjJajTYPwCAAIWY09nqdmNOZysgoCAGm9FgAgH_____BAEAAAAAAAB_HAgBAttuQgCFAIMhWv5ulxcCOgQA2AkqRnvCkz4EAAAEgOKVqHJBBFgQhUEhM-gXWqPxYDAYDAaVWVc0GBEQcJsIQLDVbrgbCFajCPj___-vCFhIBoUxGSsZFMZqFgEAdoKK0q9FLhcBAAABoHglqGgYAQ0x3M0Vq7liMpzLVtMIACjjCCAgFqdLjwA!&proto=2,3,5,6&encoded=1&pstn=vforce2&callback=&wfv=1&amp=0&qsz=15&ft=0&pb=0&pagg=101&sd=undefined&ctsldr=0&ioovp=false&distance=892&mPre=0.033&cirf=https%3A%2F%2Fabc7.com&en=1&panid=412c9ddf98b9a01877a42544fe7e185ca02cafda83b3d56a85bfe4c3a403c562
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
nginx /
Resource Hash
76cdfc7f85efc9287385cf64f7a3418e54f9f2cb8553db37f6c08c37ef275119

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
Content-type
text/plain
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
expires
Sat, 26 Jul 1997 05:00:00 GMT
x-cache
MISS
date
Sun, 06 Sep 2026 19:15:32 GMT
content-type
application/json;charset=utf-8
x-served-by
cache-lon4258-LON
x-cache-hits
0
vary
Accept-Encoding
link
<http://{"bidderRequest">; rel=preconnect
machineid
140161
cache-control
no-cache,must-revalidate,no-store,max-age=0,s-maxage=0
pragma
no-cache
x-timer
S1788722132.118384,VS0,VE302
access-control-allow-credentials
true
via
1.1 varnish
accept-ranges
bytes
access-control-allow-origin
https://abc7.com
server
nginx
GET
H2
200
cmAdService.js Show response
vidstat.taboola.com/vpaid/units/36_2_4/infra/
48 KB
0
0ms
0ms
Script
application/javascript
151.101.1.44
Fastly
General
Full URL
https://vidstat.taboola.com/vpaid/units/36_2_4/infra/cmAdService.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.1.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
AmazonS3 /
Resource Hash
1b76e60c57b71ae414a90cd7a4fd45cf10e1bf559420d4ef1f08e6dd9b40427d

Request headers

Origin
https://abc7.com
sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
"f82b0e72ca030761e5d58c4b9311405a"
age
732754
access-control-allow-methods
GET, OPTIONS, HEAD
x-cache
HIT
date
Sun, 06 Sep 2026 19:15:31 GMT
last-modified
Sat, 29 Aug 2026 07:41:28 GMT
x-served-by
cache-fra-eddf8230135-FRA
x-cache-hits
172010
content-type
application/javascript
x-amz-id-2
ed9t/Z03RjIKRHohkrxCNTc2x7anKlPX6V4MN3vkLzBnEREoehBrta5bNQjHG9DP616EpbjwzYY=
access-control-allow-headers
*
vary
Accept-Encoding
cache-control
public, max-age=2592000
x-timer
S1788722131.410572,VS0,VE0
via
1.1 varnish
x-amz-request-id
QC0549E8TNSC8TDD
accept-ranges
bytes
access-control-allow-origin
*
content-length
12238
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H2
200
st
am-vid-events.taboola.com/
0
44 B
488ms
236ms
Image
text/plain
141.226.228.48
TABOOLA-AS Tabool...
General
Full URL
https://am-vid-events.taboola.com/st?cijs=convusmp&ttype=126&cisd=convusmp&cipid=66361655&crid=-1&dast=V9kekCABYDAOCg-NNdmUJrBADgoPjTXZlCawUAAAAABgYAawcAJLRwuTymhcOt3GxGa9FuNlsLdxvLWrAaTpyDwWTiMk2GAEBCC5fLY1o43MrNZrQW7WaztXC3sawFq-HEORhMJi7TZAoAH8ZymQxqgYRl9vsOCsrp6TG7DKKi622xO5xmzxsA4tB0Onyue73C4vHNNX63X_D3nP6a0Vrt8NmdptfJ5VY5LKej4_XwutxCp-nz1ttND8vT79YcHV6n3eeWucymt-Zhd0tclrvDcnLa_W6N33U3Pd-qz8_z1jycn79iudstd4vJXg4AAAAAAA8A_____xAAAAAAABEAAAAAABIAAAAAABQAARUA_xYAAhcAAAAAABgA_____xoAAGcbAALUIAcAAr3MBoXtafsHAAAAAAAIAAAAAAAJAAAAAEAJAAAAAMAJwP________9_DMAAfeaNDMD_____DYBBDwDAgw8AwIMQAAAAQMgQwH8BxoD0hKYkEQCAwEhcEYAjgEkAnQBQAVhUAfz___dbAQBcAQAABIDilaxuZAHoDkq8hQEAAAAMjAEs0MPi95sddo3f7TKA_________38zgP8zgH80ACGAI9c0AKEFD1w1gF9AAIA1gF9AAAA2AHUD-P9_AwiAAwg7AAAAAIA7gP___389AJBbGBbD0cQ0MoxGi-XIOXPZTKaFZznYbYyjhXPhPYAcck6P7aJG8D6ACmuaXH6DpOUyGxQUv-1lkLFcJvsBTNhitJpMNsvhbLmYDIaj4Wi0P4CBWE0GCEDRksVqOVztJovRZrGYLHfD0WSCABQtGkxWo9FkMRmuRpPVbLnY7TYIQNGq1Wy0GQxXs8lst1sNB8PlaIQAE7YYrSaTzXI4Wy4mg-FoOBoNESCGFsuFx2TxrSWG5cotmngma4lhM1qrZhvPYuSamXyD1Vr0-pgei-VutFgttgggGHC4F8nTIp3INp6RxeIbOWYmw2YwW-yGy4nF5HKYhsvRxLjYWMQSzckincgu-97CsBiOJqaRYTRaLEfOmctmMi08y8FuYxwtnAt_abFceEwW31piWK7coolnspYYNqO1arbxLEaumck3WK1Fr4_psVjuRovVYt_YDYe7yWQxWe4bu-FwN5ksJst9h87wXX3ORmc1MvPo1FfZ8yPSOQwKl8HiXatOJ213eHCuDEanTP1UFnRGv9_v9_v9fr_f7zdoPQezQeE75xzG77j8knar5cfBYzAYHSaD0WE0GA2KWCK4SCcKi8dvuv1eFrfC4vGNHRaxRGm6SCd6wd9z-mtGa7XDZ3eaXieXW-WwnI6O18Prcgudps9bbzc9LE-_W3N0eJ12n1vmMpvemofdLXFZ7g7LyWn3uzV-1930fKs-P89b83B-_orlbrfcLSYTsURwukgnopfxdFG_EgAAAAAAAAAAwBLAJgAAAAAAJ0AALBcAQGL5WxcAGAQAAAAAAGAXIBoFS0e0tXDrGAAiLB6_6fZ7WdwKi8c3dlgZAEAiVpIZYDPAZwCCmNPZsgYAAAAQwAYAAAAo4wbYDcAbQIAaHAf4___3pwcAAABY2wcAYgo8cqXQC-cHKJjJajTYPwCAAIWY09nqdmNOZysgoCAGm9FgAgH_____BAEAAAAAAAB_HAgBAttuQgCFAIMhWv5ulxcCOgQA2AkqRnvCkz4EAAAEgOKVqHJBBFgQhUEhM-gXWqPxYDAYDAaVWVc0GBEQcJsIQLDVbrgbCFajCPj___-vCFhIBoUxGSsZFMZqFgEAdoKK0q9FLhcBAAABoHglqGgYAQ0x3M0Vq7liMpzLVtMIACjjCCAgFqdLjwA!&cmcv=&uv=3624&unm=INSTREAM&cb=1788722131994&abt=&su=&baseReportD=taboola.com&dataCenter=am&
Protocol
H2
Security
TLS 1.2, ECDHE_ECDSA, AES_128_GCM
Server
141.226.228.48 , Netherlands, ASN200478 (TABOOLA-AS Taboola.com ltd, IL),
Reverse DNS
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

date
Sun, 06 Sep 2026 19:15:32 GMT
server
nginx
content-length
0
GET

bdf45860-1ae7-4e9e-a093-666b40217a24
https://abc7.com/
0
0


GET
DATA
200
OK
truncated
/ Frame 079E
266 B
0
Image
image/svg+xml

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
662294921ca6240beb0f2aecb7f7ac23dd085b782bbe52a369b20226d26afe33

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/svg+xml
GET

e9c40ccf-2a85-421f-9d89-500e33c6a4d0
https://abc7.com/
0
0


GET
DATA
200
OK
truncated
/
68 B
0
Image
image/png

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
5e89733d8a8e055100cda68bf7a712ab0e1b24fefee7e39792b47cb5ff7c3cb1

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/png
POST
H2
200
event
eu.asas.yango.com/dsp/ Frame 595B
43 B
181 B
153ms
152ms
Ping
image/gif
45.87.133.75
TELETECH Edge Tec...
General
Full URL
https://eu.asas.yango.com/dsp/event?bi=mkilSgwAAAAAAAAAeJwTmKUgcVPS4rKUwywFABjkA_Q%2C&dt=3&et=3&f=xooyCeoAAAAAAAAAeJzjuN-yYll_Y8NqP4FL379dYZO49H7O9tPrFs5rYNTi4GAU4JBgUmAwkuRgEGCQYFBg0GAwYLBgcGUAAg-GAIYIBis2Dn6gFKOTJsff9rX37j5-uKpcYEbfp2UL193uPcsoARdU4khMSjbXS87PzWhmLOLj4uLoYBNiLk4slmAQYGlgZJ3EyM-BsFuANYphBiPjAkaGTYwsQGcw7mSsne17uFQiwe4g45wjChuKMiban2BkeMHI9IGR6QfjfoEGJoYOJsZJTPwcy67OuskoACYlTrAtYGJYwbTk-XwOAAd9UOo%2C&expected-method=sendBeacon&actual-method=sendBeacon
Requested by
Host: display.asas.yango.tech
URL: https://display.asas.yango.tech/ver/155/air_adaptive.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
45.87.133.75 , Serbia, ASN208398 (TELETECH Edge Technology Plus d.o.o. Beograd, RS),
Reverse DNS
Software
/
Resource Hash
548f2d6f4d0d820c6c5ffbeffcbd7f0e73193e2932eefe542accc84762deec87

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-length
57
x-yt-trace-id
7e5237cc-e987085b-3aaf95b0-3a3894fe
x-content-encoding
gzip
content-type
image/gif
content-encoding
gzip
x-yt-request-id
3dc35a9b-9fa027ad-a1123c6d-5385542e
GET
H3
200
reach_worklet.js Show response
www.googleadservices.com/pagead/managed/js/activeview/current/ Frame 90E5
196 KB
62 KB
135ms
135ms
Script
text/javascript
142.251.13.157
Google LLC
General
Full URL
https://www.googleadservices.com/pagead/managed/js/activeview/current/reach_worklet.js
Requested by
Host: www.googleadservices.com
URL: https://www.googleadservices.com/pagead/managed/js/activeview/current/reach_worklet.html
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.13.157 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
wt-in-f157.1e100.net
Software
cafe /
Resource Hash
f553d47197d2f0110392859534f34cbcefb7b47319d99151e43708c5ab3f87c1
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.googleadservices.com/pagead/managed/js/activeview/current/reach_worklet.html
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
etag
9622583581042959437
x-content-type-options
nosniff
expires
Sun, 06 Sep 2026 19:15:32 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
date
Sun, 06 Sep 2026 19:15:32 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-disposition
attachment; filename="f.txt"
cache-control
private, max-age=3600, stale-while-revalidate=3600
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
content-length
63634
x-xss-protection
0
server
cafe
GET
H2
200
license-plate Show response
login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/ Frame 4730
6 KB
3 KB
111ms
111ms
Fetch
text/x-component
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/license-plate?_rsc=193yh
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/4170-dd4027ed6752dacf.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
e8c2e0d134b3186f6147edbf89a45af57165fec36e2ff6cff0ad3dc8d9d89e85

Request headers

RSC
1
sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
Next-Router-State-Tree
%5B%22%22%2C%7B%22children%22%3A%5B%5B%22lang%22%2C%22en-US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22countryCode%22%2C%22US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22clientId%22%2C%22DATG-OTV.KABC.WEB%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%22v5%22%2C%7B%22children%22%3A%5B%22bridge%22%2C%7B%22children%22%3A%5B%22web%22%2C%7B%22children%22%3A%5B%22__PAGE__%22%2C%7B%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%2Ctrue%5D
Next-Url
/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
x-deployment-id
51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249

Response headers

x-request-id
4fb04c36159c6cbfee7da64146a014c5
cache-control
public, s-maxage=900, max-age=0, must-revalidate, stale-while-revalidate=60, stale-if-error=900
content-encoding
gzip
age
667
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
lH6RqZwLR_aoP05QbZ8tBEW8k460th0vIjc7z7vCv9eCut1mRH12hw==
date
Sun, 06 Sep 2026 19:04:25 GMT
content-type
text/x-component
vary
RSC,Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
login Show response
login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/ Frame 4730
6 KB
3 KB
112ms
112ms
Fetch
text/x-component
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/login?_rsc=193yh
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/4170-dd4027ed6752dacf.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
3218922ef139c75271887add043e4efad4e66ddaf69d1ffe9d02146976d61cb1

Request headers

RSC
1
sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
Next-Router-State-Tree
%5B%22%22%2C%7B%22children%22%3A%5B%5B%22lang%22%2C%22en-US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22countryCode%22%2C%22US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22clientId%22%2C%22DATG-OTV.KABC.WEB%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%22v5%22%2C%7B%22children%22%3A%5B%22bridge%22%2C%7B%22children%22%3A%5B%22web%22%2C%7B%22children%22%3A%5B%22__PAGE__%22%2C%7B%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%2Ctrue%5D
Next-Url
/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
x-deployment-id
51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249

Response headers

x-request-id
f82add8387f9a38aa44a597cff9ec4bf
cache-control
public, s-maxage=900, max-age=0, must-revalidate, stale-while-revalidate=60, stale-if-error=900
content-encoding
gzip
age
667
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
klnee_xIiC3gwir_4Mc-HbGXjsPwgjrny9XfVrn-96eCoutudpZ-kA==
date
Sun, 06 Sep 2026 19:04:25 GMT
content-type
text/x-component
vary
RSC,Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
login-and-recovery Show response
login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/ Frame 4730
5 KB
2 KB
112ms
112ms
Fetch
text/x-component
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/login-and-recovery?_rsc=193yh
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/4170-dd4027ed6752dacf.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
8d92fcdd3241b223a5ac2af8e8c3e6bf713a46d605d22c72107b1a6569682653

Request headers

RSC
1
sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
Next-Router-State-Tree
%5B%22%22%2C%7B%22children%22%3A%5B%5B%22lang%22%2C%22en-US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22countryCode%22%2C%22US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22clientId%22%2C%22DATG-OTV.KABC.WEB%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%22v5%22%2C%7B%22children%22%3A%5B%22bridge%22%2C%7B%22children%22%3A%5B%22web%22%2C%7B%22children%22%3A%5B%22__PAGE__%22%2C%7B%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%2Ctrue%5D
Next-Url
/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
x-deployment-id
51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249

Response headers

x-request-id
95af550fdb584f12125f665a33282a9d
cache-control
public, s-maxage=900, max-age=0, must-revalidate, stale-while-revalidate=60, stale-if-error=900
content-encoding
gzip
age
666
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
WRhqGMiY320xiAjvrewdmqyDOyS9cJM-UnfEVTrMcA3x0ADgA0_PLA==
date
Sun, 06 Sep 2026 19:04:26 GMT
content-type
text/x-component
vary
RSC,Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
login-otp Show response
login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/ Frame 4730
8 KB
3 KB
112ms
112ms
Fetch
text/x-component
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/login-otp?_rsc=193yh
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/4170-dd4027ed6752dacf.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
bbc08d49968aa7ae5d1af263634988d82d5870daa50c05cf6b0f108fe6cc3d82

Request headers

RSC
1
sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
Next-Router-State-Tree
%5B%22%22%2C%7B%22children%22%3A%5B%5B%22lang%22%2C%22en-US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22countryCode%22%2C%22US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22clientId%22%2C%22DATG-OTV.KABC.WEB%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%22v5%22%2C%7B%22children%22%3A%5B%22bridge%22%2C%7B%22children%22%3A%5B%22web%22%2C%7B%22children%22%3A%5B%22__PAGE__%22%2C%7B%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%2Ctrue%5D
Next-Url
/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
x-deployment-id
51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249

Response headers

x-request-id
09b669916d4e62f594a297a915d1824e
cache-control
public, s-maxage=900, max-age=0, must-revalidate, stale-while-revalidate=60, stale-if-error=900
content-encoding
gzip
age
666
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
Nf54DTb7b5lkcWqfZIOvUuDt9jzx7Du0Zkk2Ex3eThs0qCvx7k2Q8g==
date
Sun, 06 Sep 2026 19:04:26 GMT
content-type
text/x-component
vary
RSC,Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
logout Show response
login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/ Frame 4730
5 KB
2 KB
112ms
111ms
Fetch
text/x-component
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/logout?_rsc=193yh
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/4170-dd4027ed6752dacf.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
a2f9dde94246ee833631f377dfa88bb3f9f3f183805a17492611eb6cdf942224

Request headers

RSC
1
sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
Next-Router-State-Tree
%5B%22%22%2C%7B%22children%22%3A%5B%5B%22lang%22%2C%22en-US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22countryCode%22%2C%22US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22clientId%22%2C%22DATG-OTV.KABC.WEB%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%22v5%22%2C%7B%22children%22%3A%5B%22bridge%22%2C%7B%22children%22%3A%5B%22web%22%2C%7B%22children%22%3A%5B%22__PAGE__%22%2C%7B%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%2Ctrue%5D
Next-Url
/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
x-deployment-id
51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249

Response headers

x-request-id
01a2bab9a8969cda469ffbffff7fb032
cache-control
public, s-maxage=900, max-age=0, must-revalidate, stale-while-revalidate=60, stale-if-error=900
content-encoding
gzip
age
666
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
2C3-fL9_dEyPzcmg0vW-s5b5WwYVB0nGPqHFycMf6fca61v5lwBiDw==
date
Sun, 06 Sep 2026 19:04:26 GMT
content-type
text/x-component
vary
RSC,Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
/
trc.taboola.com/sg/thetradedesk-network/1/rtb-h/ Frame 5B9E
Redirect Chain
  • https://match.adsrvr.org/track/cmf/generic?gdpr=0&ttd_pid=054f32o&us_privacy=1NN-&ttd_tpi=1
  • https://trc.taboola.com/sg/thetradedesk-network/1/rtb-h/?taboola_hm=854f06c6-0e88-4afd-a936-6a879ff410f4
0
60 B
346ms
172ms
Image
text/plain
151.101.193.44
Fastly
General
Full URL
https://trc.taboola.com/sg/thetradedesk-network/1/rtb-h/?taboola_hm=854f06c6-0e88-4afd-a936-6a879ff410f4
Protocol
H2
Server
151.101.193.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
Referer
https://am-match.taboola.com/

Response headers

x-fastly-to-nlb-rtt
57477
x-timer
S1788722132.491046,VS0,VE59
x-vcl-time-ms
59
via
1.1 varnish
accept-ranges
bytes
x-cache
MISS
content-length
0
date
Sun, 06 Sep 2026 19:15:32 GMT
x-service-version
v1
server
nginx
x-cache-hits
0
x-served-by
cache-fra-eddf8230172-FRA

Redirect headers

location
https://trc.taboola.com/sg/thetradedesk-network/1/rtb-h/?taboola_hm=854f06c6-0e88-4afd-a936-6a879ff410f4
content-length
239
date
Sun, 06 Sep 2026 19:15:32 GMT
server
Kestrel
GET
H2
200
usync.html Show response
eus.rubiconproject.com/ Frame 194A
269 B
0
248ms
248ms
Document
text/html
23.219.139.145
Akamai Technologies
General
Full URL
https://eus.rubiconproject.com/usync.html?p=16698&endpoint=us-east&gdpr=0&us_privacy=1NN-
Requested by
Host: am-match.taboola.com
URL: https://am-match.taboola.com/sync?dast=V9FjsCABYDAOCg-NNdmUJrBADgoPjTXZlCawUAAAAABgYA9AcAJDmYGEYT02qtm7hMa9FyM1tLfBPjWrOyuCzG3WZlswyGAECSg4lhNDGt1rqJy7QWLTeztcQ3Ma41K4vLYtxtVjbLYAoAH8ZymQxqgYRl9vsOCsrp6TG7DKKi622xO5xmzxsA4tB0Onyue73C4vHNNX63X_D3nP6a0Vrt8NmdptfJ5VY5LKej4_XwutxCp-nz1ttND8vT79YcHV6n3eeWucymt-Zhd0tclrvDcnLa_W6N33U3Pd-qz8_z1jycn79iudstd4vJXg4AAAAAAA8A_____xAAAAAAABEAAAAAABIAAAAAABQAARUA_xYAAhcAAAAAABgA_____xoAAGcbAALUIAcAAr3MBoXtafsHAAAAAAAIAAAAAAAJAEBB-UwJAAAIysUJwP________9_DMAAfeaNDMD_____DYBBDwDAgw8AwIMQAAAAQMgQAIQHmcpkA5wqEQCAwIhXEYAjgEkAnQBQAVhUAfz___dbAQBcAQAABIDilayCZAHoDkq8hQEAAAAMjAEs0MPi95sddo3f7TKA_________38zgP8zgH80ACGAI9c0AKEFD1w1gF9AAIA1gF9AAAA2AHUD-P9_AwiAAwg7AAAAAIA7gP___389AJBbGBbD0cQ0MoxGi-XIOXPZTKaFZznYbYyjhXPhPYAcck6P7aJG8D6AEGGZ_b6DgnJ6eswug6joelvsDqfZcxAfNAzLySCYH8CELUaryWSzHM6Wi8lgOBqORvsDGIjVZIAAFC1ZrJbD1W6yGG0Wi8lyNxxNJghA0aLBZDUaTRaT4Wo0Wc2Wi91ugwAUrVrNRpvBcDWbzHa71XAwXI5GCDBhi9FqMtksh7PlYjIYjoaj0RABYmixXHhMFt9aYliu3KKJZ7KWGDajtWq28SxGrpnJN1itRa-P6bFY7kaL1WKLAIIBh3uRPC3SiWzjGVksvpFjZjJsBrPFbricWEwuh2m4HE2Mi41FLNGcLNKJ7LLvLQyL4WhiGhlGo8Vy5Jy5bCbTwrMc7DbG0cK58JcWy4XHZPGtJYblyi2aeCZriWEzWqtmG89i5JqZfIPVWvT6mB6L5W60WC32jd1wuJtMFpPlvrEbDneTyWKy3HfoDN_V52x0ViMzj059lT0_Ip3DoHAZLN616nTSdocH58pgdMrUT2VBZ_T7_X6_3-_3-_1-g9ZzMBsUvnPOYfyOyy9pt1p-HDwGg9FhMhgdRoPRoIglgot0orB4_Kbb72VxKywe39hhEUuUpot0ohf8Pae_ZrRWO3x2p-l1crlVDsvp6Hg9vC630Gn6vPV208Py9Ls1R4fXafe5ZS6z6a152N0Sl-XusJycdr9b43fdTc-36vPzvDUP5-evWO52y91iMhFLBKeLdCJ6GU8X9SsBAAAAAAAAAAAsAWwCAAAAAHACGMxwtlmt1glwIIvBbrRYLRcAQGL5WxcAGAQAAAAAAGAXIBoFS0e0tXDrGAAiLB6_6fZ7WdwKi8c3dlgZAEAiVpIZYDPAZwCCmNPZsgYAAAAQwAYAAAAo4wbYDcAbQIAaHAf4___3pwcAAACg3wcAghJ75EKpH-YHKJjJajTYPwCAAIWY09nqdmNOZysgoCAGm9FgAgH_____BAEAAAAAAAB_HAgBAttuQgCFAIMhWv5ulxcCOgQA2AkqRnvCkz4EAAAEgOKVqHJBBFgQhUEhM-gXWqPxYDAYDAaVWVc0GBEQcJsIQLDVbrgbCFajCPj___-vCFhIBoUxGSsZFMZqFgEAdoKK0q9FKBcBAAABoHglqGgYAQ0x3M0Vq7liMpzLVtMIACjjCCAgFqdLjwA!&excid=22&docw=0&cijs=1&nlb=false
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
23.219.139.145 Frankfurt am Main, Germany, ASN16625 (AKAMAI-AS - Akamai Technologies, Inc., US),
Reverse DNS
a23-219-139-145.deploy.static.akamaitechnologies.com
Software
Apache/2.4.65 (Debian) /
Resource Hash
e4df52d49c57bc3e7158cb052cc05c60f1258c24de5c5728dac5d43272943ad9

Request headers

Referer
https://am-match.taboola.com/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

accept-ranges
bytes
content-encoding
gzip
content-length
224
content-type
text/html
date
Sun, 06 Sep 2026 19:15:32 GMT
etag
"10d-64e67a048fd80-gzip"
last-modified
Wed, 01 Apr 2026 15:20:38 GMT
server
Apache/2.4.65 (Debian)
vary
Accept-Encoding
GET

cms
ups.analytics.yahoo.com/ups/58936/ Frame 5B9E
0
0


GET

2aa0db44-f61c-4c39-802a-d5e730c79839
https://abc7.com/
0
0


GET
H2
200
TBPrebidHandler.js Show response
vidstat.taboola.com/vpaid/vPlayer/player/v18.1.9/
233 KB
74 KB
114ms
113ms
Script
application/javascript
151.101.1.44
Fastly
General
Full URL
https://vidstat.taboola.com/vpaid/vPlayer/player/v18.1.9/TBPrebidHandler.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.1.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
AmazonS3 /
Resource Hash
67a3c609f011f84761dacd0b44576754335016e427afef6e5dd40fd132b78f18

Request headers

Origin
https://abc7.com
sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
"9c3710ca41ca81a252c2412bb58da213"
age
641940
access-control-allow-methods
GET, OPTIONS, HEAD
x-cache
HIT
date
Sun, 06 Sep 2026 19:15:32 GMT
last-modified
Sun, 30 Aug 2026 08:40:58 GMT
x-served-by
cache-fra-eddf8230135-FRA
x-cache-hits
46837
content-type
application/javascript
x-amz-id-2
gVPbuYt5uVcY/II5+vx+KQnMJ0OqsH6fPfEyZo09yZShFWwJOpkPaQVAxESaH4NTLTNW8/Jdj7BbUgvuuN9gk93xA/ejuAaR
access-control-allow-headers
*
vary
Accept-Encoding
cache-control
public, max-age=2592000
x-timer
S1788722132.264223,VS0,VE0
via
1.1 varnish
x-amz-request-id
X28MH6DY0KTJA69X
accept-ranges
bytes
access-control-allow-origin
*
content-length
75273
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H3
200
styles__rtl.css
www.gstatic.com/recaptcha/releases/8x-4t2pegToiW8KmThtO4AQt/ Frame 3444
81 KB
41 KB
61ms
61ms
Stylesheet
text/css
142.251.150.119
Google LLC
General
Full URL
https://www.gstatic.com/recaptcha/releases/8x-4t2pegToiW8KmThtO4AQt/styles__rtl.css
Requested by
Host: www.google.com
URL: https://www.google.com/recaptcha/enterprise/anchor?ar=1&k=6LcnzusZAAAAABiX7zUG2lN9BBH_1ERH1pfyR95-&co=aHR0cHM6Ly9sb2dpbi5kaXNuZXkuY29tOjQ0Mw..&hl=iw&v=8x-4t2pegToiW8KmThtO4AQt&size=invisible&anchor-ms=20000&execute-ms=30000&cb=72ilyxa5gdw7
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.150.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
057b0f165bbaef6967c56648b7db25eb5ef87716c8535055413b67e869f9b088
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.google.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
age
151531
report-to
{"group":"recaptcha-scs","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/recaptcha-scs"}]}
x-content-type-options
nosniff
expires
Sun, 05 Sep 2027 01:10:01 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sat, 05 Sep 2026 01:10:01 GMT
last-modified
Mon, 31 Aug 2026 04:01:33 GMT
content-type
text/css
vary
Accept-Encoding
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin-allow-popups; report-to="recaptcha-scs"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/recaptcha-scs
accept-ranges
bytes
content-length
42347
x-xss-protection
0
server
sffe
GET
H2
200
recaptcha__iw.js Show response
www.gstatic.com/recaptcha/releases/8x-4t2pegToiW8KmThtO4AQt/ Frame 3444
830 KB
0
0ms
0ms
Script
text/javascript
142.250.154.94
Google LLC
General
Full URL
https://www.gstatic.com/recaptcha/releases/8x-4t2pegToiW8KmThtO4AQt/recaptcha__iw.js
Requested by
Host: www.google.com
URL: https://www.google.com/recaptcha/enterprise/anchor?ar=1&k=6LcnzusZAAAAABiX7zUG2lN9BBH_1ERH1pfyR95-&co=aHR0cHM6Ly9sb2dpbi5kaXNuZXkuY29tOjQ0Mw..&hl=iw&v=8x-4t2pegToiW8KmThtO4AQt&size=invisible&anchor-ms=20000&execute-ms=30000&cb=72ilyxa5gdw7
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.250.154.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bt-in-f94.1e100.net
Software
sffe /
Resource Hash
67da984086b5b0d6fa498f8b125d3bac45ef9f195172a0bee43a52755c80718f
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.google.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
age
431943
report-to
{"group":"recaptcha-scs","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/recaptcha-scs"}]}
x-content-type-options
nosniff
expires
Wed, 01 Sep 2027 19:16:28 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Tue, 01 Sep 2026 19:16:28 GMT
last-modified
Mon, 31 Aug 2026 04:01:33 GMT
content-type
text/javascript
vary
Accept-Encoding
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin-allow-popups; report-to="recaptcha-scs"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/recaptcha-scs
accept-ranges
bytes
access-control-allow-origin
*
content-length
355787
x-xss-protection
0
server
sffe
OPTIONS
H2
204
ctr-regular
disney-entertainment.playback.edge.bamgrid.com/v7/playback/tve/ Frame
0
0
402ms
115ms
Preflight
108.138.7.109
Amazon.com
General
Full URL
https://disney-entertainment.playback.edge.bamgrid.com/v7/playback/tve/ctr-regular
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
108.138.7.109 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-108-138-7-109.fra56.r.cloudfront.net
Software
/
Resource Hash

Request headers

Accept
*/*
Access-Control-Request-Headers
authorization,content-type,x-application-version,x-bamsdk-client-id,x-bamsdk-platform,x-bamsdk-version,x-dss-edge-accept,x-dss-feature-filtering,x-request-id,x-request-yp-id
Access-Control-Request-Method
POST
Origin
https://abc7.com
Sec-Fetch-Mode
cors
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36

Response headers

access-control-allow-credentials
true
access-control-allow-headers
authorization,content-type,x-application-version,x-bamsdk-client-id,x-bamsdk-platform,x-bamsdk-version,x-dss-edge-accept,x-dss-feature-filtering,x-request-id,x-request-yp-id
access-control-allow-methods
GET, POST, PUT, PATCH, DELETE, OPTIONS
access-control-allow-origin
https://abc7.com
access-control-expose-headers
x-request-id, x-bamtech-region, date
access-control-max-age
600
age
3104
cache-control
public, max-age=3600
date
Sun, 06 Sep 2026 18:23:48 GMT
vary
origin,access-control-request-headers
via
1.1 5c0a79476717d213b9c559bafee1c65e.cloudfront.net (CloudFront)
x-amz-cf-id
T0FWYHmQ7RcuYoM_MngUFQxN_okhXa_v7ufNasBi3S9NkqCsBuiABQ==
x-amz-cf-pop
FRA56-P6
x-bamtech-region
eu-central-1
x-cache
Hit from cloudfront
x-request-id
187a395c6316f93fd28694a1280398fa
HEAD

ads.c9b27fd9a37506f0a7de49b2c12ee4b1.json
static-assets.bamgrid.com/config/adserve/adsimage/banner-ad/VideoAd/adBlockDetector/
0
0


GET
H2
200
P96F99720-5612-425A-A2B3-CE301EC6CC95.js Show response
cdn-gl.imrworldwide.com/conf/
41 KB
8 KB
403ms
133ms
Script
application/javascript
13.32.121.65
Amazon.com
General
Full URL
https://cdn-gl.imrworldwide.com/conf/P96F99720-5612-425A-A2B3-CE301EC6CC95.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.32.121.65 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-32-121-65.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
689dfcaa410812ccc5ba4350a29f2fbe51a02a3a247f3e5d55cd30357a2f9098

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
cache-control
max-age=86400,s-maxage=86400
content-encoding
gzip
x-amz-version-id
x_b7NZqXCNdaWACGHyNHH5YBSWcQhaqV
etag
W/"dd00adeb10fb57650205a8b367978e14"
age
2775
via
1.1 cb0a9b0d01a1b0cc9278d9875ce23c92.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
813zUgmgTT7edIeqnQZKTUvbfCb5QNfzAm7EKRT534yAKdi0lnePOQ==
date
Sun, 06 Sep 2026 18:30:22 GMT
content-type
application/javascript
last-modified
Sun, 06 Sep 2026 17:18:41 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P1
x-amz-server-side-encryption
AES256
POST
H2
200
ctr-regular Show response
disney-entertainment.playback.edge.bamgrid.com/v7/playback/tve/
13 KB
4 KB
269ms
268ms
Fetch
application/json
108.138.7.109
Amazon.com
General
Full URL
https://disney-entertainment.playback.edge.bamgrid.com/v7/playback/tve/ctr-regular
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
108.138.7.109 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-108-138-7-109.fra56.r.cloudfront.net
Software
/
Resource Hash
89617350dfdae309c8f6bc45f636eaa3e472bb15723d3f7cf3c65ff7bda68cde

Request headers

x-application-version
1.3
x-request-id
c1a455c8-29a9-4d6f-9410-75ac709bd13a
authorization
Bearer eyJpc3MiOiJodHRwczovL2xvZ2luLmRpc25leS5jb20iLCJ0eXAiOiJhdCtqd3QiLCJhbGciOiJFZERTQSIsImtpZCI6Ikh1Ti03Ti1vWFNLa0pDYVVISjZ0aTFKT3IwS1VQTi1pMG56Ung5SXNNSDQifQ.eyJzdWIiOiJmMmFkYTk0ZC0zMmE3LTQ3NDAtOWU0Mi05ZDA4YWNhODk3M2YiLCJzY3AiOlsib3BlbmlkIiwic3RyZWFtaW5nIiwiYXBpOmlkZW50aXR5OnVzZXIud3JpdGUiXSwic3VidCI6ImFub255bW91cyIsImRldmljZV9pZCI6ImYyYWRhOTRkLTMyYTctNDc0MC05ZTQyLTlkMDhhY2E4OTczZiIsImlzcyI6Imh0dHBzOi8vbG9naW4uZGlzbmV5LmNvbSIsImNsaWVudF9pZCI6IkRUQ0ktQUJDTkVXU19MQS1PUC1UT0tFTi5HQy5TRVJWRVIiLCJzaWQiOiJkNjFmZTc3Yi0yYzMyLTQwMDItYTU1ZC02NzQ4NDllMzY4NWEiLCJhdWQiOiJEVENJLUFCQ05FV1NfTEEtT1AtVE9LRU4uR0MuU0VSVkVSIiwibmJmIjoxNzg4NzIyMTMwLCJ1ZGMiOiJleUo2YVhBaU9pSkVSVVlpTENKcmFXUWlPaUl6ZEUxaE5XRTFRazFDT0hRMWRrOW1WVU10VTFOTlYwaDVhelZmVkZCS2NsOXFibkI0UTNSbmNtWlJJaXdpWTNSNUlqb2lTazlUUlN0S1UwOU9JaXdpZEhsd0lqb2lZWFFyYW5kMElpd2laVzVqSWpvaVdFTXlNRkFpTENKaGJHY2lPaUprYVhJaWZRLi5mREtyWUh5QzR1dHhGd1dnYXJmTXBsRjU0SXFHVGd0eS5obkVmM2FicmV2Qjh5X2JXbDFzbGticHpmVEpfdGZDOUxZenpXWUtnMDdCb1Z2My0xWEhhSWIwZ1NNbnBXeENEM3VESHAyX0tWWU1CN2hJZUFTVzdGdHM5YV95cWR0b05scE15OC12cXlaOTZEU0JLb1FLWU1yQWs3ZXBDdllSQmdlZ3RnODJvRnBFTHg5eVNsMVRReEhCcXVzT0p5UEVYcmZVekU4NjlpY3dvUm5VdWJOZDlxMmsyUUdRLXg1bUROakoxUHRrZUpaeTV1NzhLR0NXRUNnV3ZDdlB5d2NMX3J6aTdob3V1VmNGaTNfN01sR2puU0NkaTNKclJLNV9HX1lxc0Jwd05oNHJBN3FwVV82NTBmTXVITHFpRVFod0E5bHJGR2ZRUlNkdzhmZzhrNlVST0p4SGpQbHM5dENnaXVjMGNxMHN4Skg0emFUTHZtZElQNHFCRnFrU00zMXJ5Nmk2dUNsemNmbU4zUGp0MmljMDV0b1hIazN0R0JwM2IyS09UMnJXTVdPV2w3X1RqYjlqWGY5R05GQU10OHBxU3A3Q29RV09IZFplM0lvZlF5OVdQVmJaLXpoUEZsYzNsVXR2dC01aC1aS1FrRlo1Y0tJTmEtSTdVckcwbThrLXBRUWxxQU1yVW5tX3FSbUFrYXVQYkYxTFJkb2tNd0FMbmhhZUtLQ2xLNHBnSDBXZmxTMHhfY2ZrbnBmbkd6MzBzMjFtWWNzX0xIcmdHU3RoZG1DU3I1WG52Z1VMVHNuR2Y3a1ZkaTRRbGIzeFVvVk5LanFjWTc3aTBDYk1OU0NweDg4S1RhbW5kSGdkamRkZzVHLW9XcldZSjNsLWg0RkRWOTAxN05TS3p0QWUybm5jV05aaEl2blN6Z2dFYURvOHUwdzNoemg0cXFWRUV1UTFYWFRQbjFsemZ0cllVN18wWkJGelAyQWRfS09aLXktNUZES2UyUlZqcFNxWWhPM19WVzlyNTRlQV9UX0hNaVJwTklQNi1UcjI4Z2xfZkd0a1hnaENlVEhXUHR4WnIxSzh3QTB2RHRQM1NNUXFjajhQc19QUkVVZFc2MUZZR3JmNlB0UGJ3STFBU2hHTTJtVmdjaGJWM1RyZENMMFp3c1hnVEQxR3N2Z1hEYXA1OHFnYTN4RVNycTdubmVRLVkzQV8tUEdBYW5uMFhGUHY0Y2Jyc25TVUN2VFpvYzQ4eXZHYzdSTjZKY0lINVpvSkpHVTFvaHJJMzFOTE1kX1FDV0NIMWxrVEtHNmV5Z0JQbDlYR01sS0RmQXpVZGUyenpNWWg3T0IyODB5cUVTTjFnd2RBb2R0VDFNRXJ0aVZWalJvWjRtNF93X2VtQ2tIa0ZQY0VTY1lrN1hFaGxpRURBaHd4amxVcWdMYmMtQ0hQZlpVQ2pqV2xQcXNnTVlVSjFRTVItR2gxVEZjTjRoRHVVMEZKZk53T0gtaldJZ0F4UFFjbkNZaEFuLUlwN1NVd0N5TTRKMTV4WG51TzVpMEREM2lEWUJZZUtYbDZxMndfMGtkdGJRdmo4Y0RlRk9Hdi1vU2FoU0pSSXpWajRPcFdVam9oYlcxV1MzeTl0TjJNd2g1RVVHYnpobkdOSGxEQkI0VEZDbU44c2dYMnJSenRVcWotVUJ2aDJPcFg2cG95Skp4S19Dd2pPZk9Pd25UUUpVa0x4U19TUUk2aWhMWjFpVnpKSmh5M3FGTThMQ3gwcFZGRXFRcHVQSFNSMHNNMVdILTFNQlhGRGJrZlpzX3hLUUlJWlNtVVBvNnFBTy1xWFdiRUdlc3BiUnRlR3pzUEIwV0Z6cEI3UGRJY3Bna1VUUmR5R18wVWpPZ1BTc1dLVC10LVNtSDJ2X1lIS0hfcFhIX1NLemY0djY5dnlFYXgxYjRoZHhpOWVodGhaRXlnUi1rMWlvNUg2bFRlYWtVTENpX0pFaG5yVVZoWTEyS1BudTVQdTBocXVzN0pDOHpBVmlicEVUM0xaMERHcUFYeVdtOVV0cWRvaGFPMzZBYzlUbWJXaUxvSFFzZ0NzSDVUT3hESVFSS19qYVNOZ0hNcHk2RFJmcExFZmpNdkVlTE9LblU3YW1GbGRWS1I5VjF5c041VWVfWjlTVUU5Z2ZXQXFQSUZtRjNJQTFKYng0Rzc3SG8tWlV0NEdwdWhtUFNCeW9GWEh4TF8wTm5ESHZKaHdmWnM0MFA3U041WUFHelJvVlgwLXlHbzlqZlY2ZGdjVmthdy1BM3kxdjVsUVNTNXNBMkJmZFgwYmhuS3BTcVJwRHQzcDRaeEFjbnpkR2lQX01nWEw0SzNmZzZlZkEtS0xzUTM1Qm1WNVljLTFKblRuNHhoc0tmWjJmUXdidGRNVjJLeHNSQWJFOG10TWZzM0N6UDZxWnV1UXZGamlPNzJaZzlCYkJ2S3NhUlNzQkRXdVB2anpJYmMuU0l5eWFMMm9EVlo3SUNCNngzQ1U1ZyIsImF1dGhfdGltZSI6MTc4ODcyMjEyOSwiZXhwIjoxNzg4NzM2NTMwLCJpYXQiOjE3ODg3MjIxMzAsImp0aSI6IklELmY2YTAzYmZjLWFkZTctNDQ0Ni1hZjFmLWQ4NWE1NzY2ZjI4YSJ9.fnf_mVNa1DVlPlkzYnFdyPGY70-8TDnhQAYW9XOPi-0hySFg8zr2nO4hYIcQgDhWNORfTp61ZIKraMmbLRjrBA
sec-ch-ua-platform
"Linux"
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
accept
application/vnd.media-service+json
content-type
application/json
x-dss-feature-filtering
true
Referer
https://abc7.com/
x-request-yp-id
624b805dafc5c73635b1a216
x-bamsdk-client-id
abc_news_los_angeles-d652ef7d
x-bamsdk-version
35.3
x-bamsdk-platform
javascript/linux/chrome
x-dss-edge-accept
vnd.dss.edge+json; version=2
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36

Response headers

access-control-max-age
600
x-request-id
c1a455c8-29a9-4d6f-9410-75ac709bd13a
access-control-expose-headers
x-request-id, x-bamtech-region, date
content-encoding
gzip
access-control-allow-methods
GET, POST, PUT, PATCH, DELETE, OPTIONS
x-cache
Miss from cloudfront
x-amz-cf-id
pFg4P3ijIUa1OVNgvTfYbJP_-ly6zIodqH6qy36KvcyOk-875JscfA==
date
Sun, 06 Sep 2026 19:15:32 GMT
content-type
application/json
vary
origin, access-control-request-headers
cache-control
no-store
access-control-allow-credentials
true
x-bamtech-region
eu-central-1
via
1.1 5c0a79476717d213b9c559bafee1c65e.cloudfront.net (CloudFront)
access-control-allow-origin
https://abc7.com
x-amz-cf-pop
FRA56-P6
HEAD

ads.c9b27fd9a37506f0a7de49b2c12ee4b1.json
static-assets.bamgrid.com/config/adserve/adsimage/banner-ad/VideoAd/adBlockDetector/
0
0


POST
H2
200
asset Show response
watch.auth.api.espn.com/video/auth/media/19779896/
1 KB
992 B
636ms
238ms
XHR
application/json
44.193.192.39
Amazon.com
General
Full URL
https://watch.auth.api.espn.com/video/auth/media/19779896/asset?context=news_kabc&aspectRatio=16x9&pbo=true&apikey=uiqlbgzdwuru14v627vdusswb
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
44.193.192.39 Ashburn, United States, ASN14618 (AMAZON-AES - Amazon.com, Inc., US),
Reverse DNS
ec2-44-193-192-39.compute-1.amazonaws.com
Software
/
Resource Hash
641a57088c34291a9040d39db376615c677a0ef720c72bdb575215b5955651fb

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
Content-Type
application/x-www-form-urlencoded;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=0, no-cache, no-store, must-revalidate
content-encoding
gzip
pragma
no-cache
access-control-allow-credentials
true
via
1.1 e805860bb79f (Varnish/7.5)
expires
0
access-control-allow-origin
https://abc7.com
date
Sun, 06 Sep 2026 19:15:32 GMT
content-type
application/json
vary
Accept-Encoding
GET
H3
204
sodar
pagead2.googlesyndication.com/pagead/ Frame 6174
0
17 B
289ms
166ms
Image
image/
142.251.127.155
Google LLC
General
Full URL
https://pagead2.googlesyndication.com/pagead/sodar?id=sodar2&v=255&li=gpt_m202609010101&jk=8843972379179831&rc=
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.127.155 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfrai-in-f155.1e100.net
Software
cafe /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.google.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

timing-allow-origin
*
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
0
date
Sun, 06 Sep 2026 19:15:32 GMT
x-xss-protection
0
content-type
image/
server
cafe
GET
H/1.1
200
OK
19779720_090226-kabc-ontario-quake-tn.jpg
cdn.abcotvs.com/dip/images/
85 KB
86 KB
880ms
550ms
Image
image/jpeg
23.36.162.16
AKAMAI-ASN1 Akama...
General
Full URL
https://cdn.abcotvs.com/dip/images/19779720_090226-kabc-ontario-quake-tn.jpg
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_256_GCM
Server
23.36.162.16 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a23-36-162-16.deploy.static.akamaitechnologies.com
Software
/
Resource Hash
e3efaf1295ee82d8a470e95c65709fedfa402e39da822d164cec74cac5658555

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

Transfer-Encoding
chunked
X-Varnish
283782730
Accept-Ranges
bytes
Date
Sun, 06 Sep 2026 19:15:33 GMT
Content-Type
image/jpeg
Connection
keep-alive, Transfer-Encoding
POST
H/1.1
202
Accepted
rum Show response
browser-intake-datadoghq.com/api/v2/ Frame 4730
53 B
464 B
259ms
256ms
Fetch
application/json
3.233.158.26
Amazon.com
General
Full URL
https://browser-intake-datadoghq.com/api/v2/rum?ddsource=browser&ddtags=sdk_version%3A5.31.1%2Capi%3Afetch%2Cenv%3Aprod%2Cservice%3Aidentity-ui%2Cversion%3A51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249&dd-api-key=pub3b1d5b26d9b77ebcdf2e8ba26cc9f858&dd-evp-origin-version=5.31.1&dd-evp-origin=browser&dd-request-id=afc0ca47-1ae2-4820-9889-d2c9d7ef6368&dd-evp-encoding=deflate&batch_time=1788722132302
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/4170-dd4027ed6752dacf.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_128_GCM
Server
3.233.158.26 Ashburn, United States, ASN14618 (AMAZON-AES - Amazon.com, Inc., US),
Reverse DNS
ec2-3-233-158-26.compute-1.amazonaws.com
Software
/
Resource Hash
9ef4074096268f618d1b2dc9443ef83ebcc0ac1369a69dafa97accbedef1a779
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
Content-Type
text/plain
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains; preload
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
access-control-allow-origin
*
content-length
53
accept-encoding
identity,gzip,x-gzip,deflate,x-deflate,zstd
date
Sun, 06 Sep 2026 19:15:32 GMT
content-type
application/json
dd-request-id
afc0ca47-1ae2-4820-9889-d2c9d7ef6368
GET
H2
200
7135-5f2d30eb5af67570.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
6 KB
2 KB
107ms
107ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/7135-5f2d30eb5af67570.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
f3f56123666fc97561414fd4c9fbf530a1330f1b699a5084b41313815f016536

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
76e953767bfe3ebf6922e0d1fb506c7d
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"168b-1a01fc3c5d8"
age
1473341
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
u0QqtpZ0k3ediJnOnEhi8ZGUJWESGrKf1xVOTDGrdFO_VVE9wq5_fA==
date
Thu, 20 Aug 2026 17:59:51 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
page-ed89a17ac6a4877e.js Show response
login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/license-plate/ Frame 4730
2 KB
1 KB
108ms
107ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/license-plate/page-ed89a17ac6a4877e.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
f4f8e0561c0afde3829a1e235fc5a4ee5b5d779f0a68333ba187f6da8579dda3

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
8eece20acf55b4a8f3752151309fe932
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"617-1a05f957328"
age
266760
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
SbEqVrMveBMAy7AltGvNyCeWoS7DH9958HLrgILG-uTyY0X8tLtQnQ==
date
Thu, 03 Sep 2026 17:09:32 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
9026-b7d0f1f25ca76135.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
9 KB
4 KB
109ms
109ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/9026-b7d0f1f25ca76135.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
a54fcbbee5eda9b409f4435a796e6423e2373547df9d1b16e370c51b67bcbd36

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
5a08ef74cdbb1cbb47cc2db54d0e202b
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"2551-1a01fc3c5d8"
age
1473341
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
Pi1I0ziDDC40YaY6CBNots6PJBwUQ75Go0_DUeFjedsBva9VJKwHsA==
date
Thu, 20 Aug 2026 17:59:51 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
page-7718e80119136706.js Show response
login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/login/ Frame 4730
16 KB
7 KB
111ms
110ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/login/page-7718e80119136706.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
b36a68027d17f5457211db8d034053b4cafe221ca87bdaa7737a42bfca3d2922

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
09f62aea2453d286e8c77f05c6b1961c
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"3ffa-1a05f957328"
age
266760
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
FFLJFjOKaa2bbD9_7Z0fv0TcAe-y-pI3XjfC7ObpmlP_0K-J4txQlQ==
date
Thu, 03 Sep 2026 17:09:32 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
page-fd51369b88a5d369.js Show response
login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/login-and-recovery/ Frame 4730
19 KB
10 KB
112ms
112ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/login-and-recovery/page-fd51369b88a5d369.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
ac729cabb5437ad91bcc7463e05be0b847358b9c0a1a7a4fba42c1c63b655819

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
7b4baeb8030680e927a3a74aa47df506
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"4db8-1a05f957328"
age
267031
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
olU7ZZT8XxKnYGtiGYWdzKvkopYv5JMzredMJ06DY7R9m554e1hQ_w==
date
Thu, 03 Sep 2026 17:05:01 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
5154-b05ec7862ba5e685.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
6 KB
3 KB
113ms
112ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/5154-b05ec7862ba5e685.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
6ea7bd10dfc6c3cfe5006e1251c4505141c9400e273d94040122cfe47ae95574

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
600f5e26e08db10f1813f0f1d8db46dc
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"176b-1a01fc3c5d8"
age
1473341
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
oTUnHGR8NNnaZmPcpiavz8c2arnBgDkH-QocKovm0recvW_xhOl-DA==
date
Thu, 20 Aug 2026 17:59:51 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
9773-2052515445a253ae.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
56 KB
21 KB
113ms
113ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/9773-2052515445a253ae.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
1a67e0764ce075829e6aa35b659a8aff1ab4ed14ae21df5c769c4795121b0001

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
b263e8faef39682e65192ee02a131544
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"dfad-1a05f957328"
age
266797
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
_V0T2A7OM5pOqd3KSDEtRs-YQGfrZZmOuIY2bIuAQSi3n6hKbfn8EA==
date
Thu, 03 Sep 2026 17:08:55 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
7071-3a894b9b02d9e9a3.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
18 KB
7 KB
114ms
114ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/7071-3a894b9b02d9e9a3.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
6242e7715d5a78fb862a20dbc97d0de5bd71ea4fd54029323cd907f5e810f9ac

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
0d04235b61e5ad2234807ce7bb7defcf
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"4853-1a05f957328"
age
266825
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
F9C3cxRcspNM-W2261j8y4XRqchV9-GeRZ9sT_QaQOrTYgo3VSo3jQ==
date
Thu, 03 Sep 2026 17:08:27 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
page-ddf5e36d19ce5898.js Show response
login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/login-otp/ Frame 4730
14 KB
6 KB
115ms
114ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/login-otp/page-ddf5e36d19ce5898.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
274d5ee299f505c0c77f73f04da184db2bac264d6ce7dd76680778547e1668ff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
2813a1fe2f2e3f1b3a83d15c472118b5
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"362f-1a05f957328"
age
266825
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
iTXXNS_1i4H2nRLK1WvRO5UwSIhZO_atUrzBoRYInBDiFdLSrYLZkw==
date
Thu, 03 Sep 2026 17:08:27 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
layout-9cd225b200ed4033.js Show response
login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/login-otp/ Frame 4730
2 KB
1 KB
115ms
114ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/login-otp/layout-9cd225b200ed4033.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
6eefc05b9fe3d5f31b3d501714985a22338c59e1c6f11a68f3b4fbdd7c8ede86

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
39f2cae3a34305412fb4d22344140a4f
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"962-1a01fc3c5d8"
age
1473341
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
JZ_BUZOAx-5aDMdjfZ7JA-W56bmtnabqIDjKgLP15Mchk8qhBbdsiQ==
date
Thu, 20 Aug 2026 17:59:51 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
page-c5102d5334d45a71.js Show response
login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/logout/ Frame 4730
51 KB
22 KB
161ms
160ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/logout/page-c5102d5334d45a71.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
3be19625c87e4050796ac75492788007e168a27d7fe72c33fcef8f2759adc303

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
ce826db8ee0d3e90f69d4bf5c19c5fcb
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"cb99-1a05f957328"
age
266783
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
inijlY4ML9eqrRHl2Oo0LlKa7WD2xW_h0etpnSRadPwmjebT2eogrw==
date
Thu, 03 Sep 2026 17:09:09 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H3
200
H4tXIWzGmRRUuIDhC3tbHWx4M6eCYgM3ypneUZtoV5s.js Show response
pagead2.googlesyndication.com/bg/ Frame F978
57 KB
22 KB
194ms
116ms
Script
text/javascript
142.251.127.155
Google LLC
General
Full URL
https://pagead2.googlesyndication.com/bg/H4tXIWzGmRRUuIDhC3tbHWx4M6eCYgM3ypneUZtoV5s.js
Requested by
Host: ep2.adtrafficquality.google
URL: https://ep2.adtrafficquality.google/sodar/sodar2/255/runner.html
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.127.155 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfrai-in-f155.1e100.net
Software
sffe /
Resource Hash
1f8b57216cc6991454b880e10b7b5b1d6c7833a782620337ca99de519b68579b
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://ep2.adtrafficquality.google/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
320793
report-to
{"group":"botguard-scs","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/botguard-scs"}]}
x-content-type-options
nosniff
expires
Fri, 03 Sep 2027 02:08:59 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 03 Sep 2026 02:08:59 GMT
last-modified
Mon, 24 Aug 2026 10:08:00 GMT
content-type
text/javascript
vary
Accept-Encoding
cache-control
public, max-age=31536000
cross-origin-opener-policy
same-origin; report-to="botguard-scs"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/botguard-scs
accept-ranges
bytes
content-length
22260
x-xss-protection
0
server
sffe
GET

webworker.js
www.google.com/recaptcha/enterprise/ Frame 3444
0
0


POST
H2
201
sessions Show response
abcotv.hb-api.omtrdc.net/api/v1/
76 B
337 B
431ms
192ms
XHR
text/plain
63.140.62.236
Amazon.com
General
Full URL
https://abcotv.hb-api.omtrdc.net/api/v1/sessions
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
63.140.62.236 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ip-63-140-62-236.data.adobedc.net
Software
jag /
Resource Hash
39233deb9216d05661ac4509010e5f4aa838874e97e16e0093da2ac3dff6fa66
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

access-control-expose-headers
Location
cache-control
no-cache, no-store, max-age=0, no-transform, private
location
/api/v1/sessions/43b9cbd5d2f6ba6370bb2e0aa2926d521920638e15fc27a7b9dbc0d6a149de3c
x-content-type-options
nosniff
access-control-allow-origin
*
content-length
76
date
Sun, 06 Sep 2026 19:15:32 GMT
x-xss-protection
1; mode=block
content-type
text/plain; charset=UTF-8
server
jag
GET
H2
200
usync.js Show response
eus.rubiconproject.com/ Frame B2F1
46 KB
12 KB
127ms
127ms
Script
text/html
23.219.139.145
Akamai Technologies
General
Full URL
https://eus.rubiconproject.com/usync.js
Requested by
Host: eus.rubiconproject.com
URL: https://eus.rubiconproject.com/usync.html?p=16698&endpoint=us-east&gdpr=0&us_privacy=1NN-
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
23.219.139.145 Frankfurt am Main, Germany, ASN16625 (AKAMAI-AS - Akamai Technologies, Inc., US),
Reverse DNS
a23-219-139-145.deploy.static.akamaitechnologies.com
Software
Apache/2.4.65 (Debian) / PHP/8.3.24
Resource Hash
848a360b8078c658fe7f07e24557e2e6f86a019de3c3834359a21849d8c6d877

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://eus.rubiconproject.com/usync.html?p=16698&endpoint=us-east&gdpr=0&us_privacy=1NN-
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=49353
content-encoding
gzip
expires
Mon, 07 Sep 2026 08:58:05 GMT
p3p
CP="NOI CURa ADMa DEVa TAIa OUR # BUS IND UNI COM NAV INT"
content-length
11678
date
Sun, 06 Sep 2026 19:15:32 GMT
last-modified
Sun, 06 Sep 2026 08:58:05 GMT
x-powered-by
PHP/8.3.24
server
Apache/2.4.65 (Debian)
content-type
text/html;charset=UTF-8
vary
Accept-Encoding
GET
H2
200
usync.js Show response
eus.rubiconproject.com/ Frame 194A
46 KB
0
124ms
124ms
Script
text/html
23.219.139.145
Akamai Technologies
General
Full URL
https://eus.rubiconproject.com/usync.js
Requested by
Host: eus.rubiconproject.com
URL: https://eus.rubiconproject.com/usync.html?p=16698&endpoint=us-east&gdpr=0&us_privacy=1NN-
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
23.219.139.145 Frankfurt am Main, Germany, ASN16625 (AKAMAI-AS - Akamai Technologies, Inc., US),
Reverse DNS
a23-219-139-145.deploy.static.akamaitechnologies.com
Software
Apache/2.4.65 (Debian) / PHP/8.3.24
Resource Hash
848a360b8078c658fe7f07e24557e2e6f86a019de3c3834359a21849d8c6d877

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://eus.rubiconproject.com/usync.html?p=16698&endpoint=us-east&gdpr=0&us_privacy=1NN-
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=49353
content-encoding
gzip
expires
Mon, 07 Sep 2026 08:58:05 GMT
p3p
CP="NOI CURa ADMa DEVa TAIa OUR # BUS IND UNI COM NAV INT"
content-length
11678
date
Sun, 06 Sep 2026 19:15:32 GMT
last-modified
Sun, 06 Sep 2026 08:58:05 GMT
x-powered-by
PHP/8.3.24
server
Apache/2.4.65 (Debian)
content-type
text/html;charset=UTF-8
vary
Accept-Encoding
GET
H2
200
TBrubiconPrebidHandler.js Show response
vidstat.taboola.com/vpaid/vPlayer/player/v18.1.9/
166 KB
55 KB
112ms
111ms
Script
application/javascript
151.101.1.44
Fastly
General
Full URL
https://vidstat.taboola.com/vpaid/vPlayer/player/v18.1.9/TBrubiconPrebidHandler.js
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.1.44 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
AmazonS3 /
Resource Hash
3ed66a20857ca5f52a3ff0e25bdfa394f7a23d369532722fe8865df520eebb85

Request headers

Origin
https://abc7.com
sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
"050f54e8fa853bdd8553268c9a621099"
age
641939
access-control-allow-methods
GET, OPTIONS, HEAD
x-cache
HIT
date
Sun, 06 Sep 2026 19:15:32 GMT
last-modified
Sun, 30 Aug 2026 08:40:59 GMT
x-served-by
cache-fra-eddf8230135-FRA
x-cache-hits
21766
content-type
application/javascript
x-amz-id-2
xjbQfkzsXApR45aK8jYZxPbRfYuk0dEbucJM/D5XjxYbSwIJMeuRMDntBZxKIQ5kFiHMbSNS2YA=
access-control-allow-headers
*
vary
Accept-Encoding
cache-control
public, max-age=2592000
x-timer
S1788722132.482543,VS0,VE0
via
1.1 varnish
x-amz-request-id
7CKZQ0KKSM1WBDAE
accept-ranges
bytes
access-control-allow-origin
*
content-length
56228
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H3
200
logo_48.png
www.gstatic.com/recaptcha/api2/ Frame 3444
2 KB
2 KB
62ms
61ms
Image
image/png
142.251.150.119
Google LLC
General
Full URL
https://www.gstatic.com/recaptcha/api2/logo_48.png
Requested by
Host: www.gstatic.com
URL: https://www.gstatic.com/recaptcha/releases/8x-4t2pegToiW8KmThtO4AQt/styles__rtl.css
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.150.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
1b9efb22c938500971aac2b2130a475fa23684dd69e43103894968df83145b8a
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.gstatic.com/recaptcha/releases/8x-4t2pegToiW8KmThtO4AQt/styles__rtl.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

age
211439
report-to
{"group":"recaptcha-scs","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/recaptcha-scs"}]}
x-content-type-options
nosniff
expires
Fri, 11 Sep 2026 08:31:33 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 04 Sep 2026 08:31:33 GMT
last-modified
Tue, 03 Mar 2020 20:15:00 GMT
content-type
image/png
cache-control
public, max-age=604800
cross-origin-opener-policy
same-origin-allow-popups; report-to="recaptcha-scs"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/recaptcha-scs
accept-ranges
bytes
content-length
2228
x-xss-protection
0
server
sffe
GET
H3
200
KFO7CnqEu92Fr1ME7kSn66aGLdTylUAMa3yUBA.woff2
fonts.gstatic.com/s/roboto/v48/ Frame 3444
39 KB
39 KB
113ms
113ms
Font
font/woff2
142.251.14.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/roboto/v48/KFO7CnqEu92Fr1ME7kSn66aGLdTylUAMa3yUBA.woff2
Requested by
Host: www.google.com
URL: https://www.google.com/recaptcha/enterprise/anchor?ar=1&k=6LcnzusZAAAAABiX7zUG2lN9BBH_1ERH1pfyR95-&co=aHR0cHM6Ly9sb2dpbi5kaXNuZXkuY29tOjQ0Mw..&hl=iw&v=8x-4t2pegToiW8KmThtO4AQt&size=invisible&anchor-ms=20000&execute-ms=30000&cb=72ilyxa5gdw7
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.14.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f94.1e100.net
Software
sffe /
Resource Hash
20b535fa80c8189e3b87d1803038389960203a886d502bc2ef1857affc2f38d2
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://www.google.com
sec-ch-ua-platform
"Linux"
Referer
https://www.google.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

age
169614
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Sat, 04 Sep 2027 20:08:38 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 04 Sep 2026 20:08:38 GMT
last-modified
Thu, 29 May 2025 23:30:55 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
40128
x-xss-protection
0
server
sffe
GET
H2
200
mobile-number Show response
login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/ Frame 4730
8 KB
3 KB
107ms
107ms
Fetch
text/x-component
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/mobile-number?_rsc=193yh
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/4170-dd4027ed6752dacf.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
74bb14323272dd2a12566add0bffa3bcd1778935e74d2da70e98a1d7d338af80

Request headers

RSC
1
sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
Next-Router-State-Tree
%5B%22%22%2C%7B%22children%22%3A%5B%5B%22lang%22%2C%22en-US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22countryCode%22%2C%22US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22clientId%22%2C%22DATG-OTV.KABC.WEB%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%22v5%22%2C%7B%22children%22%3A%5B%22bridge%22%2C%7B%22children%22%3A%5B%22web%22%2C%7B%22children%22%3A%5B%22__PAGE__%22%2C%7B%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%2Ctrue%5D
Next-Url
/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
x-deployment-id
51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249

Response headers

x-request-id
d9be065c8cd4f3aa092024a804e0ac34
cache-control
public, s-maxage=900, max-age=0, must-revalidate, stale-while-revalidate=60, stale-if-error=900
content-encoding
gzip
age
666
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
uSRTbj8A4nD8koJOSpXHTrMV4xeFQuAQJl4nJk63LDkW1jlnuMpB1A==
date
Sun, 06 Sep 2026 19:04:26 GMT
content-type
text/x-component
vary
RSC,Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
parent-invite-sent Show response
login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/ Frame 4730
6 KB
2 KB
107ms
107ms
Fetch
text/x-component
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/parent-invite-sent?_rsc=193yh
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/4170-dd4027ed6752dacf.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
af79d724c1a0a17ff8b8142d7cf7e58125144a5a564dc52969e4aff6a90fbfcb

Request headers

RSC
1
sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
Next-Router-State-Tree
%5B%22%22%2C%7B%22children%22%3A%5B%5B%22lang%22%2C%22en-US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22countryCode%22%2C%22US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22clientId%22%2C%22DATG-OTV.KABC.WEB%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%22v5%22%2C%7B%22children%22%3A%5B%22bridge%22%2C%7B%22children%22%3A%5B%22web%22%2C%7B%22children%22%3A%5B%22__PAGE__%22%2C%7B%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%2Ctrue%5D
Next-Url
/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
x-deployment-id
51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249

Response headers

x-request-id
422f666f76bc30671acea2dc2d08f475
cache-control
public, s-maxage=900, max-age=0, must-revalidate, stale-while-revalidate=60, stale-if-error=900
content-encoding
gzip
age
666
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
wMy7GGVyJ8pdWqkDhWPXcU9fxDB5dMYkgax0QCIxI66VcSzOWE5EOw==
date
Sun, 06 Sep 2026 19:04:26 GMT
content-type
text/x-component
vary
RSC,Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
parent-registration-invite Show response
login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/ Frame 4730
6 KB
3 KB
109ms
109ms
Fetch
text/x-component
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/parent-registration-invite?_rsc=193yh
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/4170-dd4027ed6752dacf.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
d5f454da7bbedd9d0b2ce15f0ba501a042d503bd745c3a4a1aea4b5ac38da0c3

Request headers

RSC
1
sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
Next-Router-State-Tree
%5B%22%22%2C%7B%22children%22%3A%5B%5B%22lang%22%2C%22en-US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22countryCode%22%2C%22US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22clientId%22%2C%22DATG-OTV.KABC.WEB%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%22v5%22%2C%7B%22children%22%3A%5B%22bridge%22%2C%7B%22children%22%3A%5B%22web%22%2C%7B%22children%22%3A%5B%22__PAGE__%22%2C%7B%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%2Ctrue%5D
Next-Url
/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
x-deployment-id
51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249

Response headers

x-request-id
a5dd57ccc50be2036cb74dba5a410893
cache-control
public, s-maxage=900, max-age=0, must-revalidate, stale-while-revalidate=60, stale-if-error=900
content-encoding
gzip
age
666
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
iUN1SHGFdlTKQ7pc39GCIJN_lhnbz_N6LKvzJnJnbK29vI2IQFb-tA==
date
Sun, 06 Sep 2026 19:04:26 GMT
content-type
text/x-component
vary
RSC,Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
password Show response
login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/ Frame 4730
8 KB
3 KB
108ms
108ms
Fetch
text/x-component
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/password?_rsc=193yh
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/4170-dd4027ed6752dacf.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
03a35c301ec459be605ccfede17c83c8f5cac3c8391d1f00f86fa60d306f6a1b

Request headers

RSC
1
sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
Next-Router-State-Tree
%5B%22%22%2C%7B%22children%22%3A%5B%5B%22lang%22%2C%22en-US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22countryCode%22%2C%22US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22clientId%22%2C%22DATG-OTV.KABC.WEB%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%22v5%22%2C%7B%22children%22%3A%5B%22bridge%22%2C%7B%22children%22%3A%5B%22web%22%2C%7B%22children%22%3A%5B%22__PAGE__%22%2C%7B%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%2Ctrue%5D
Next-Url
/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
x-deployment-id
51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249

Response headers

x-request-id
daee7acef92dcba77aa87a981a301c44
cache-control
public, s-maxage=900, max-age=0, must-revalidate, stale-while-revalidate=60, stale-if-error=900
content-encoding
gzip
age
666
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
swgP319Z3jnzlnW5YiRnkA5bzfVIw1yhF-uaA_PmmZFUWYPQluR7sA==
date
Sun, 06 Sep 2026 19:04:26 GMT
content-type
text/x-component
vary
RSC,Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H3
204
gen_204
pagead2.googlesyndication.com/pagead/ Frame 595B
0
0
159ms
159ms
Fetch
image/gif
142.251.127.157
Google LLC
General
Full URL
https://pagead2.googlesyndication.com/pagead/gen_204?id=av-js&type=colleague-executed&name=1
Requested by
Host: pagead2.googlesyndication.com
URL: https://pagead2.googlesyndication.com/pagead/managed/js/activeview/current/ufs_web_display.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.127.157 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfrai-in-f157.1e100.net
Software
cafe /
Resource Hash
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
0
date
Sun, 06 Sep 2026 19:15:32 GMT
x-xss-protection
0
content-type
image/gif
server
cafe
GET
H3
204
gen_204
pagead2.googlesyndication.com/pagead/ Frame 595B
0
0
159ms
159ms
Fetch
image/gif
142.251.127.157
Google LLC
General
Full URL
https://pagead2.googlesyndication.com/pagead/gen_204?id=av-js&type=reach&proto=CAlgAWACYANgBGgD
Requested by
Host: pagead2.googlesyndication.com
URL: https://pagead2.googlesyndication.com/pagead/managed/js/activeview/current/ufs_web_display.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.127.157 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfrai-in-f157.1e100.net
Software
cafe /
Resource Hash
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
0
date
Sun, 06 Sep 2026 19:15:32 GMT
x-xss-protection
0
content-type
image/gif
server
cafe
GET
H2
200
model_person_country_code_IL_person_region_code_494c.json Show response
www.googletagservices.com/agrp/prod/ Frame 90E5
640 KB
90 KB
347ms
114ms
Fetch
application/json
142.251.14.155
Google LLC
General
Full URL
https://www.googletagservices.com/agrp/prod/model_person_country_code_IL_person_region_code_494c.json
Requested by
Host: www.googleadservices.com
URL: https://www.googleadservices.com/pagead/managed/js/activeview/current/reach_worklet.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.14.155 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f155.1e100.net
Software
sffe /
Resource Hash
851e1aa83430dd145496fa705ee41fedd762ef3ff27368ab63377312b49e97fc
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/ads-people-metrics-releaser
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.googleadservices.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
age
86233
report-to
{"group":"ads-people-metrics-releaser","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/ads-people-metrics-releaser"}]}
x-content-type-options
nosniff
expires
Sun, 06 Sep 2026 19:18:19 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sat, 05 Sep 2026 19:18:19 GMT
last-modified
Tue, 30 Jul 2024 19:25:57 GMT
content-type
application/json
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/ads-people-metrics-releaser
cache-control
public, max-age=86400
cross-origin-opener-policy
same-origin; report-to="ads-people-metrics-releaser"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
content-length
91065
x-xss-protection
0
server
sffe
POST
H3
200
report-shared-storage
www.googleadservices.com/.well-known/private-aggregation/ Frame 90E5
0
0
155ms
155ms
Fetch
text/html
142.251.13.157
Google LLC
General
Full URL
https://www.googleadservices.com/.well-known/private-aggregation/report-shared-storage
Requested by
Host: www.googleadservices.com
URL: https://www.googleadservices.com/pagead/managed/js/activeview/current/reach_worklet.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.13.157 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
wt-in-f157.1e100.net
Software
cafe /
Resource Hash
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.googleadservices.com/pagead/managed/js/activeview/current/reach_worklet.html
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

timing-allow-origin
*
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
0
date
Sun, 06 Sep 2026 19:15:32 GMT
x-xss-protection
0
content-type
text/html; charset=UTF-8
server
cafe
POST
H3
200
report-shared-storage
www.googleadservices.com/.well-known/private-aggregation/ Frame 90E5
0
0
155ms
154ms
Fetch
text/html
142.251.13.157
Google LLC
General
Full URL
https://www.googleadservices.com/.well-known/private-aggregation/report-shared-storage
Requested by
Host: www.googleadservices.com
URL: https://www.googleadservices.com/pagead/managed/js/activeview/current/reach_worklet.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.13.157 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
wt-in-f157.1e100.net
Software
cafe /
Resource Hash
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.googleadservices.com/pagead/managed/js/activeview/current/reach_worklet.html
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

timing-allow-origin
*
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
0
date
Sun, 06 Sep 2026 19:15:32 GMT
x-xss-protection
0
content-type
text/html; charset=UTF-8
server
cafe
GET
H3
204
gen_204
pagead2.googlesyndication.com/pagead/ Frame 90E5
0
0
282ms
160ms
Fetch
image/gif
142.251.127.155
Google LLC
General
Full URL
https://pagead2.googlesyndication.com/pagead/gen_204?id=av-js&type=reach&proto=CAESDk9wZXJhdGlvbkVycm9yGlRGYWlsZWQgdG8gZXhlY3V0ZSAnYWRkTW9kdWxlJyBvbiAnU2hhcmVkU3RvcmFnZVdvcmtsZXQnOiBTaGFyZWQgU3RvcmFnZSBpcyBkaXNhYmxlZC4%3D
Requested by
Host: www.googleadservices.com
URL: https://www.googleadservices.com/pagead/managed/js/activeview/current/reach_worklet.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.127.155 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfrai-in-f155.1e100.net
Software
cafe /
Resource Hash
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.googleadservices.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
0
date
Sun, 06 Sep 2026 19:15:32 GMT
x-xss-protection
0
content-type
image/gif
server
cafe
GET
H/1.1
200
OK
score.omid.min.js Show response
js.ad-score.com/
16 KB
6 KB
113ms
113ms
Script
text/javascript
18.245.60.26
Amazon.com
General
Full URL
https://js.ad-score.com/score.omid.min.js?pid=1000075
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_128_GCM
Server
18.245.60.26 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-18-245-60-26.fra60.r.cloudfront.net
Software
/
Resource Hash
0477e91b2a6ae684ee4053ea3aa3b2e5f053b218174dd748c5227711473c9963

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

Content-Encoding
gzip
Age
18296
Access-Control-Allow-Methods
GET
X-Cache
Hit from cloudfront
X-Amz-Cf-Id
03bGqQRHh0EOvv-aIFrLkVQCNcNWQYRic6U_eKB0Jct-p3Ivd0ci1A==
Date
Sun, 06 Sep 2026 14:10:36 GMT
Content-Type
text/javascript; charset=utf-8
Last-Modified
Wed, 19 Aug 2026 19:55:53 GMT
Transfer-Encoding
chunked
Cache-Control
public, max-age=86400
Connection
keep-alive
Access-Control-Allow-Credentials
true
Via
1.1 69a82a9746d3a7343dca651e0829f000.cloudfront.net (CloudFront)
Accept-Ranges
bytes
Access-Control-Allow-Origin
*
X-Amz-Cf-Pop
FRA60-P5
GET
H2
200
address Show response
login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/ppu/ Frame 4730
6 KB
3 KB
107ms
107ms
Fetch
text/x-component
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/interaction/ppu/address?_rsc=193yh
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/4170-dd4027ed6752dacf.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
980734d1c32ed1fd0f67ba83c86679c05d6250300b61b934a8716b8745e5b03e

Request headers

RSC
1
sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
Next-Router-State-Tree
%5B%22%22%2C%7B%22children%22%3A%5B%5B%22lang%22%2C%22en-US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22countryCode%22%2C%22US%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%5B%22clientId%22%2C%22DATG-OTV.KABC.WEB%22%2C%22d%22%5D%2C%7B%22children%22%3A%5B%22v5%22%2C%7B%22children%22%3A%5B%22bridge%22%2C%7B%22children%22%3A%5B%22web%22%2C%7B%22children%22%3A%5B%22__PAGE__%22%2C%7B%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%5D%7D%2Cnull%2Cnull%2Ctrue%5D
Next-Url
/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
x-deployment-id
51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249

Response headers

x-request-id
36080ccc13795353e78c3ffe1b6b0093
cache-control
public, s-maxage=900, max-age=0, must-revalidate, stale-while-revalidate=60, stale-if-error=900
content-encoding
gzip
age
666
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
_EhjDXeaStpM-tyvq2_XGjrN9lZstyzCtrAqDe-F8fbTL_zgmyfLtA==
date
Sun, 06 Sep 2026 19:04:26 GMT
content-type
text/x-component
vary
RSC,Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
DATA
200
OK
truncated
/
35 B
0
Image
image/gif

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
6adc3d4c1056996e4e8b765a62604c78b1f867cceb3b15d0b9bedb7c4857f992

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/gif
POST
H2
200
auction Show response
prebid-server.rubiconproject.com/openrtb2/
184 B
207 B
361ms
114ms
Fetch
application/json
69.173.144.137
Magnite
General
Full URL
https://prebid-server.rubiconproject.com/openrtb2/auction
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
69.173.144.137 , Germany, ASN26667 (RUBICONPROJECT - Magnite, Inc., US),
Reverse DNS
Software
/
Resource Hash
9ecdbb81669f15a9368bb0fce834f80e2c3b1a81063170139ad3d22a7e8f0302

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
content-type
text/plain
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, no-store, must-revalidate
content-encoding
gzip
pragma
no-cache
access-control-allow-credentials
true
expires
0
access-control-allow-origin
https://abc7.com
content-length
173
x-prebid
pbs-java/4.1.0
content-type
application/json
vary
origin
POST
H2
200
auction Show response
prebid-server.rubiconproject.com/openrtb2/
184 B
332 B
358ms
113ms
Fetch
application/json
69.173.144.137
Magnite
General
Full URL
https://prebid-server.rubiconproject.com/openrtb2/auction
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
69.173.144.137 , Germany, ASN26667 (RUBICONPROJECT - Magnite, Inc., US),
Reverse DNS
Software
/
Resource Hash
ab05b13067a2c08f88ecdb041b8fbe96f75532860b958f783c0ea39311a5dc70

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
content-type
text/plain
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, no-store, must-revalidate
content-encoding
gzip
pragma
no-cache
access-control-allow-credentials
true
expires
0
access-control-allow-origin
https://abc7.com
content-length
173
x-prebid
pbs-java/4.1.0
content-type
application/json
vary
origin
POST
H2
200
auction Show response
prebid-server.rubiconproject.com/openrtb2/
184 B
208 B
409ms
167ms
Fetch
application/json
69.173.144.137
Magnite
General
Full URL
https://prebid-server.rubiconproject.com/openrtb2/auction
Requested by
Host: abc7.com
URL: https://abc7.com/post/34-magnitude-earthquake-hits-ontario-shaking-felt-san-bernardino-county-usgs-says/19779712/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
69.173.144.137 , Germany, ASN26667 (RUBICONPROJECT - Magnite, Inc., US),
Reverse DNS
Software
/
Resource Hash
1f54e4067b5f8d343d39e211ffde7c80f443f882f83a7d9ddcdbb3a8f8ef0f51

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://abc7.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
content-type
text/plain
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, no-store, must-revalidate
content-encoding
gzip
pragma
no-cache
access-control-allow-credentials
true
expires
0
access-control-allow-origin
https://abc7.com
content-length
174
x-prebid
pbs-java/4.1.0
content-type
application/json
vary
origin
GET
H/1.1
200
OK
khaos.json Show response
token.rubiconproject.com/ Frame B2F1
7 B
1 KB
511ms
127ms
XHR
application/json
69.173.144.165
Magnite
General
Full URL
https://token.rubiconproject.com/khaos.json?gdpr=0&us_privacy=1NN-
Requested by
Host: eus.rubiconproject.com
URL: https://eus.rubiconproject.com/usync.js
Protocol
HTTP/1.1
Security
TLS 1.2, RSA, AES_256_GCM
Server
69.173.144.165 , Germany, ASN26667 (RUBICONPROJECT - Magnite, Inc., US),
Reverse DNS
Software
/
Resource Hash
a1dd48c657971696c2087f2a6beb489ee65b25320b763222f10718dd93e9149e

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://eus.rubiconproject.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

Cache-Control
no-cache,no-store,must-revalidate
Pragma
no-cache
access-control-allow-credentials
true
Expires
0
access-control-allow-origin
https://eus.rubiconproject.com
P3P
CP="NOI CURa ADMa DEVa TAIa OUR BUS IND UNI COM NAV INT"
X-RPHost
9b9ca48f3d05737dc119d72e271168fa
content-length
7
content-type
application/json; charset=UTF-8
GET
H/1.1
200
OK
khaos.json Show response
token.rubiconproject.com/ Frame 194A
7 B
1 KB
635ms
125ms
XHR
application/json
69.173.144.165
Magnite
General
Full URL
https://token.rubiconproject.com/khaos.json?gdpr=0&us_privacy=1NN-
Requested by
Host: eus.rubiconproject.com
URL: https://eus.rubiconproject.com/usync.js
Protocol
HTTP/1.1
Security
TLS 1.2, RSA, AES_256_GCM
Server
69.173.144.165 , Germany, ASN26667 (RUBICONPROJECT - Magnite, Inc., US),
Reverse DNS
Software
/
Resource Hash
a1dd48c657971696c2087f2a6beb489ee65b25320b763222f10718dd93e9149e

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://eus.rubiconproject.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

Cache-Control
no-cache,no-store,must-revalidate
Pragma
no-cache
access-control-allow-credentials
true
Expires
0
access-control-allow-origin
https://eus.rubiconproject.com
P3P
CP="NOI CURa ADMa DEVa TAIa OUR BUS IND UNI COM NAV INT"
X-RPHost
9b9ca48f3d05737dc119d72e271168fa
content-length
7
content-type
application/json; charset=UTF-8
GET
H2
200
page-3516c4af42b6396c.js Show response
login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/mobile-number/ Frame 4730
36 KB
12 KB
108ms
107ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/mobile-number/page-3516c4af42b6396c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
c077e4f796211b9f94f35efac2c60c5b7614249e8a39caa36e5616390df7a64a

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
190404661242b2a169fc8f7e9a9b352b
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"8e72-1a05f957328"
age
266787
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
FhA80cL_kbizHqAlRB71ll6zDAa4cXUus5Jl8EXb1vwJcTUkvxC7vQ==
date
Thu, 03 Sep 2026 17:09:05 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
page-fa34bc6b4dbf764d.js Show response
login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/parent-invite-sent/ Frame 4730
31 KB
13 KB
108ms
108ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/parent-invite-sent/page-fa34bc6b4dbf764d.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
6dc75cc4dcd7060b9a49d23200245dd3ba5bdc2952ed9b600013680be1559d28

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
f41157572a781d2c44fb754947499ad6
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"7a29-1a05f957328"
age
266740
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
KOfKyj4m5BKSCyrT2bx4tppDNB280wf9oi9DN3xMDEF1KQTq7Unn1A==
date
Thu, 03 Sep 2026 17:09:52 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
page-93fb7b1ab89548bf.js Show response
login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/parent-registration-invite/ Frame 4730
8 KB
4 KB
108ms
108ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/parent-registration-invite/page-93fb7b1ab89548bf.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
47fd60176c91f7c0c20e55e17ae0f7e16216d352dc1268862b32c05c73da1534

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
17e8dfca571f6b552c27baadd083d5bc
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"1fd2-1a05f957328"
age
266772
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
3ilJJU1kg-FYA1Q9AZw_0y7QgrDFg8VacxXgN5Q-9LDAvYQhnvX7UA==
date
Thu, 03 Sep 2026 17:09:20 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
4512-ecd858de4a150594.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
3 KB
2 KB
108ms
108ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/4512-ecd858de4a150594.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
1d988f4ccc50c9ac66cdfea786a534663997ff41b4670652154cb9270d5d390e

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
6c92117cb84c324db7dfb2c65fd3176e
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"d7f-1a01fc3c5d8"
age
1473342
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
FBeEfsZBQbOno5W-vFJSpVM13hA84uhYKnEgyXrU8fvJ_z29h7T_xg==
date
Thu, 20 Aug 2026 17:59:50 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
4010-1fbd50bd187fc087.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
58 KB
25 KB
110ms
109ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/4010-1fbd50bd187fc087.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
a34fbc6ec3e4a418632cdbbcc19e4e84521f8f74ebaeffac606380e8b1e20082

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
9f0893bcb33a8308909adb3e210d0bbe
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"e80d-1a05f957328"
age
266774
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
moWtZ0gPi0yq8LFsTPy9zrL0dKRy9gXlK4V1QSqyK_H-Msaz5zX5Cg==
date
Thu, 03 Sep 2026 17:09:18 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
page-c3fa10589e428a2f.js Show response
login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/password/ Frame 4730
6 KB
3 KB
110ms
110ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/password/page-c3fa10589e428a2f.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
028dec4eeb6e29dc643f8afead5b401396ec51237a066ae37f9278725ea09750

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
03c6c89fc0e0c6d5b943720b00a78670
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"19d5-1a05f957328"
age
266774
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
33dvTOJxnfyI3LScLTgWIJ7-w4HwWiw_5sqtbYOcP-OamfvCBaKAKQ==
date
Thu, 03 Sep 2026 17:09:18 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
3274-5f36a5154db4c447.js Show response
login.disney.com/_next/static/chunks/ Frame 4730
7 KB
3 KB
106ms
106ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/3274-5f36a5154db4c447.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
86532c53b3bcb78b269365acbf576b013a1a5832699eec67f56ca11b9639253f

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
c0941e3da20b8b3d014dc0ab11c4bd9d
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"1dd2-1a01fc3c5d8"
age
1473342
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
AT47D16PjINxwoUIVUIZ7eSawPZfs7sMdmozqrMu6kFxgwdKYj5GBg==
date
Thu, 20 Aug 2026 17:59:50 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 20 Aug 2026 15:21:59 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
200
page-63821278730f968a.js Show response
login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/ppu/address/ Frame 4730
19 KB
7 KB
107ms
107ms
Script
application/javascript
3.161.82.115
Amazon.com
General
Full URL
https://login.disney.com/_next/static/chunks/app/%5Blang%5D/%5BcountryCode%5D/%5BclientId%5D/interaction/ppu/address/page-63821278730f968a.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Requested by
Host: login.disney.com
URL: https://login.disney.com/_next/static/chunks/webpack-1c192558414fa53c.js?dpl=51a0b6f1e58b690cb1e6fa0a2446ba23bd37e249
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.115 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-115.fra56.r.cloudfront.net
Software
/
Resource Hash
103236443157c99e73de959ad94516e14f95a1a920f29e3c950742056efee8c6

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://login.disney.com/en-US/US/DATG-OTV.KABC.WEB/v5/bridge/web
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

x-request-id
3f37b0eefd274bd7ffda28f2028c24f8
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
etag
W/"4c42-1a05f957328"
age
267072
x-bamtech-region
eu-central-1
via
1.1 fb02145a1ed983434aacfc27d3e4a9a6.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
x-amz-cf-id
zm9o5qBNnUxzVQW7BkNJaAES7IfN8o4Q7X3uOfX1j46-5w6bIFV2GQ==
date
Thu, 03 Sep 2026 17:04:20 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 02 Sep 2026 00:47:05 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P10
GET
H2
204
generate_204
ep2.adtrafficquality.google/ Frame F978
0
40 B
113ms
112ms
Image
text/plain
142.251.14.132
Google LLC
General
Full URL
https://ep2.adtrafficquality.google/generate_204?RGIzLg
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.14.132 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f132.1e100.net
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://ep2.adtrafficquality.google/sodar/sodar2/255/runner.html
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
0
date
Sun, 06 Sep 2026 19:15:32 GMT
cross-origin-resource-policy
cross-origin
GET
H2
200
nlsSDK600.bundle.min.js