Submitted URL:
https://ahddong.org/ 4yr old
Effective URL:
https://erhassa.com/ 2yr old
Submission: On September 09 via api (September 9th 2026, 5:42:00 am UTC) from BE — Scanned from SG

Summary

This website contacted 7 IPs in 3 countries across 8 domains to perform 41 HTTP transactions. The main IP is 159.89.206.1, located in Singapore, Singapore and belongs to DIGITALOCEAN-ASN - DigitalOcean, LLC, US. The main domain is erhassa.com. 2yr old
TLS certificate: Issued by YR2 on September 9th 2026. Valid for: 3mo.
This is the only time erhassa.com was scanned on urlscan.io!

urlscan.io Verdict: No classification

Domain & IP information

IP Address AS Autonomous System
1 2 159.89.206.1 159.89.206.1 14061 (DIGITALOC...) (DIGITALOCEAN-ASN - DigitalOcean)
4 167.99.66.65 167.99.66.65 14061 (DIGITALOC...) (DIGITALOCEAN-ASN - DigitalOcean)
22 2a06:98c1:310... 2a06:98c1:3103::6812:26a1 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
2 2404:6800:400... 2404:6800:4003:c11::61 15169 (GOOGLE) (GOOGLE - Google LLC)
9 142.251.156.119 142.251.156.119 15169 (GOOGLE) (GOOGLE - Google LLC)
1 2404:6800:400... 2404:6800:4003:c01::65 15169 (GOOGLE) (GOOGLE - Google LLC)
2 2404:6800:400... 2404:6800:4003:c11::8b 15169 (GOOGLE) (GOOGLE - Google LLC)
41 7
Apex Domain
Subdomains
Transfer
22 teepublic.com
assets.teepublic.com — Cisco Umbrella Rank: 36984 8yr old
386 KB
8 google.com
www.google.com — Cisco Umbrella Rank: 6 14yr old
apis.google.com — Cisco Umbrella Rank: 265 10yr old
179 KB
4 in.net
gambar.caramel.in.net 3mo old
324 KB
3 gstatic.com
www.gstatic.com — Cisco Umbrella Rank: 9 10yr old
3 KB
2 googletagmanager.com
www.googletagmanager.com — Cisco Umbrella Rank: 86 14yr old
339 KB
1 google-analytics.com
www.google-analytics.com — Cisco Umbrella Rank: 151 14yr old
1 erhassa.com
erhassa.com 2yr old
71 KB
1 ahddong.org 1 redirects
ahddong.org 4yr old
419 B
41 8
Domain Requested by
22 assets.teepublic.com erhassa.com
assets.teepublic.com
6 www.google.com erhassa.com
www.google.com
4 gambar.caramel.in.net erhassa.com
3 www.gstatic.com www.google.com
2 apis.google.com www.google.com
apis.google.com
2 www.googletagmanager.com erhassa.com
www.google.com
1 www.google-analytics.com www.googletagmanager.com
1 erhassa.com
1 ahddong.org 1 redirects
41 9
Subject Issuer Validity Valid
erhassa.com
YR2
2026-09-09 -
2026-12-08
3mo crt.sh
gambar.caramel.in.net
YR1
2026-08-31 -
2026-11-29
3mo crt.sh
assets.teepublic.com
WE1
2026-08-09 -
2026-11-07
3mo crt.sh
*.google-analytics.com
WR2
2026-08-10 -
2026-11-02
3mo crt.sh
*.google.com
WR2
2026-08-10 -
2026-11-02
3mo crt.sh
*.apis.google.com
WR2
2026-08-10 -
2026-11-02
3mo crt.sh

This page contains 2 frames:

Primary Page: https://erhassa.com/
Frame ID: 00A84AFE01AFF33D730B3AE2C84B10DB
Requests: 29 HTTP requests in this frame

Frame: https://www.google.com/shopping/customerreviews/badge?usegapi=1&merchant_id=107797987&position=INLINE&hl=en_US&origin=https%3A%2F%2Fwww.teepublic.com&gsrc=3p&jsh=m%3B%2F_%2Fscs%2Fabc-static%2F_%2Fjs%2Fk%3Dgapi.lb.en.8uXxGUoumbY.O%2Fd%3D1%2Frs%3DAHpOoo96qx3mL4tzGUOa-0q0udyPRqEAoA%2Fm%3D__features__
Frame ID: 6563EAA2DDB6D616DE84C6610E9784B9
Requests: 12 HTTP requests in this frame

Screenshot

Page Title

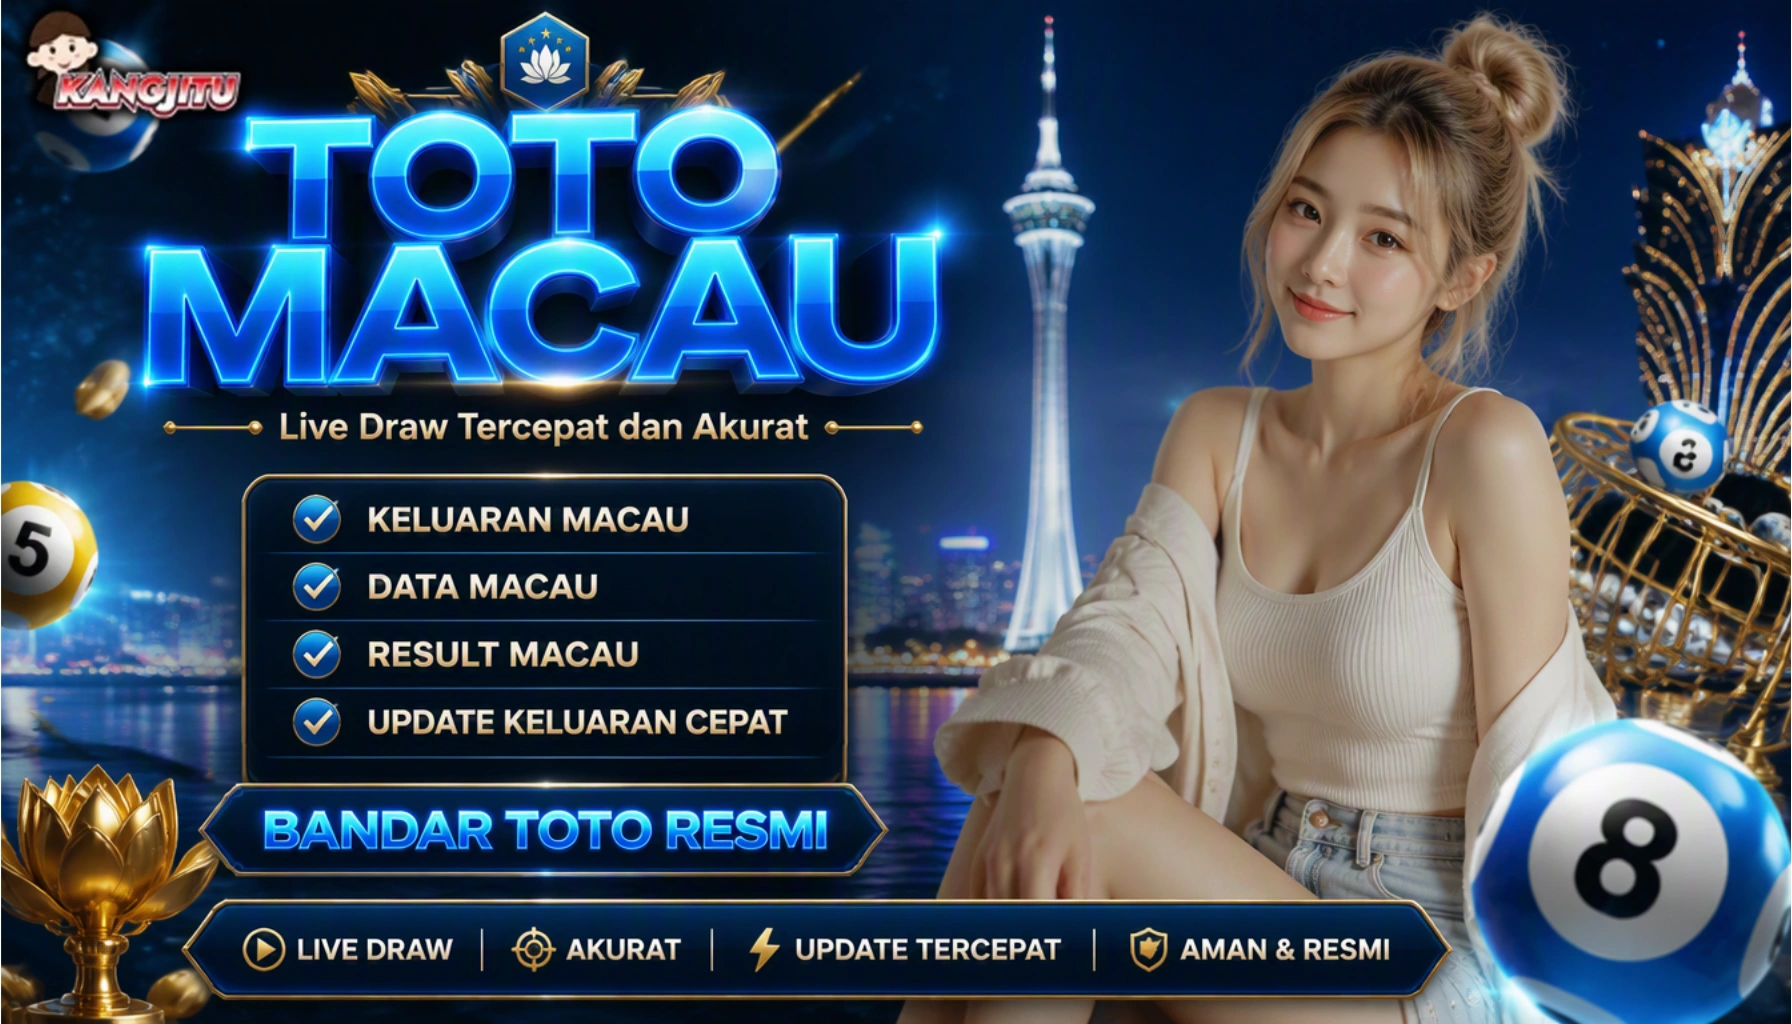
Paito Toto Macau 4D, Data & Keluaran Toto Macau Terbaru Result Akurat | KANGJITU

Page URL History Show full URLs

  1. https://ahddong.org/ HTTP 301
    https://erhassa.com/ Page URL

Detected technologies

(JavaScript frameworks)
Overall confidence: 100%
Detected patterns
  • <link rel="amphtml"

(JavaScript frameworks)
Overall confidence: 100%
Detected patterns
  • <[^>]+data-controller

(Security)
Overall confidence: 100%
Detected patterns

(Analytics)
Overall confidence: 100%
Detected patterns
  • googletagmanager\.com/gtag/js

(Tag managers)
Overall confidence: 100%
Detected patterns
  • \.googletagmanager\.com/

Page Statistics

41
Requests

100 %
HTTPS

57 %
IPv6

8
Domains

9
Subdomains

7
IPs

3
Countries

1302 kB
Transfer

3287 kB
Size

4
Cookies

Page URL History

This captures the URL locations of the websites, including HTTP redirects and client-side redirects via JavaScript or Meta fields.

  1. https://ahddong.org/ HTTP 301
    https://erhassa.com/ Page URL

Redirected requests

There were HTTP redirect chains for the following requests:

41 HTTP transactions
0 data transactions

Method
Protocol
Status Resource
Path
Size
x-fer
Time
Latency
Type
MIME-Type
IP
Location
GET
H2
200
Primary Request / Show response
erhassa.com/
Redirect Chain
  • https://ahddong.org/
  • https://erhassa.com/
378 KB
71 KB
35ms
4ms
Document
text/html
159.89.206.1
DigitalOcean
General
Full URL
https://erhassa.com/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
159.89.206.1 Singapore, Singapore, ASN14061 (DIGITALOCEAN-ASN - DigitalOcean, LLC, US),
Reverse DNS
Software
nginx /
Resource Hash
97ac201ffb076c59e7fd1e7ba2417e21b22d5bdfc4796265069f57cef05ce542
Security Headers
Name Value
Strict-Transport-Security max-age=31536000

Request headers

Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

alt-svc
quic=":443"; h3=":443"; h3-29=":443"; h3-27=":443";h3-25=":443"; h3-T050=":443"; h3-Q050=":443";h3-Q049=":443";h3-Q048=":443"; h3-Q046=":443"; h3-Q043=":443"
content-encoding
gzip
content-type
text/html
date
Wed, 09 Sep 2026 05:42:01 GMT
etag
W/"6aa0dfa8-5e7bb"
last-modified
Wed, 09 Sep 2026 04:25:12 GMT
server
nginx
strict-transport-security
max-age=31536000
vary
Accept-Encoding

Redirect headers

alt-svc
quic=":443"; h3=":443"; h3-29=":443"; h3-27=":443";h3-25=":443"; h3-T050=":443"; h3-Q050=":443";h3-Q049=":443";h3-Q048=":443"; h3-Q046=":443"; h3-Q043=":443"
content-length
162
content-type
text/html
date
Wed, 09 Sep 2026 05:42:01 GMT
location
https://erhassa.com/
server
nginx
strict-transport-security
max-age=31536000
GET
H2
200
kangjitu-totomacau4.webp
gambar.caramel.in.net/uploads/KANGJITU/
318 KB
319 KB
156ms
6ms
Image
image/webp
167.99.66.65
DigitalOcean
General
Full URL
https://gambar.caramel.in.net/uploads/KANGJITU/kangjitu-totomacau4.webp
Requested by
Host: erhassa.com
URL: https://erhassa.com/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
167.99.66.65 Singapore, Singapore, ASN14061 (DIGITALOCEAN-ASN - DigitalOcean, LLC, US),
Reverse DNS
Software
nginx /
Resource Hash
899c1986f49fb1ff2436782e5f792471c5b7b290f43141e044c36cd7c9651696
Security Headers
Name Value
Strict-Transport-Security max-age=31536000

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://erhassa.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
etag
"6a92f590-4f8fe"
accept-ranges
bytes
content-length
325886
date
Wed, 09 Sep 2026 05:42:01 GMT
content-type
image/webp
last-modified
Sat, 29 Aug 2026 15:06:56 GMT
server
nginx
GET
H2
200
product-27efacddfffc4e9541c100011b9e0cf4258b53d4bd8386ac5e37135f3cd07974.css
assets.teepublic.com/assets/bundles/
315 KB
48 KB
192ms
58ms
Stylesheet
text/plain
2a06:98c1:3103::6812:26a1
Cloudflare
General
Full URL
https://assets.teepublic.com/assets/bundles/product-27efacddfffc4e9541c100011b9e0cf4258b53d4bd8386ac5e37135f3cd07974.css
Requested by
Host: erhassa.com
URL: https://erhassa.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a06:98c1:3103::6812:26a1 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
30ac72b3a0780512f20d9702968b2ae6182c055f63b2bd87606deef0a8c170ed
Security Headers
Name Value
Strict-Transport-Security max-age=15768000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://erhassa.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=15768000; includeSubDomains; preload
cache-control
public, max-age=14400
timing-allow-origin
https://www.teepublic.com
content-encoding
gzip
cf-cache-status
HIT
etag
W/"ce577d891c0a2871264608c382372e02"
age
2667
cf-ray
a383de02ee786014-SIN
expires
Wed, 09 Sep 2026 09:42:01 GMT
date
Wed, 09 Sep 2026 05:42:01 GMT
last-modified
Wed, 24 Sep 2025 18:06:40 GMT
vary
Accept-Encoding
server
cloudflare
GET
H2
200
Roobert-Medium-88ba78029f73fa9f18e1e3c31c1f076acdc49223af70a78b2ea4bdbab8168283.woff2
assets.teepublic.com/assets/
30 KB
30 KB
205ms
59ms
Font
font/woff2
2a06:98c1:3103::6812:26a1
Cloudflare
General
Full URL
https://assets.teepublic.com/assets/Roobert-Medium-88ba78029f73fa9f18e1e3c31c1f076acdc49223af70a78b2ea4bdbab8168283.woff2
Requested by
Host: erhassa.com
URL: https://erhassa.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a06:98c1:3103::6812:26a1 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
7364e8d42eb65f4df96e9b6a25dfe8832b1d7ccc8bf7983f958cff809b912ebb
Security Headers
Name Value
Strict-Transport-Security max-age=15768000; includeSubDomains; preload

Request headers

Origin
https://erhassa.com
sec-ch-ua-platform
"Linux"
Referer
https://erhassa.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=15768000; includeSubDomains; preload
cache-control
public, max-age=14400
timing-allow-origin
https://www.teepublic.com
content-encoding
gzip
cf-cache-status
HIT
etag
W/"18b3097c5b0830cabe0fcb94972c9042"
age
4515
cf-ray
a383de02fd49fd3f-SIN
expires
Wed, 09 Sep 2026 09:42:01 GMT
access-control-allow-origin
*
date
Wed, 09 Sep 2026 05:42:01 GMT
content-type
font/woff2
last-modified
Mon, 17 Jul 2023 18:35:13 GMT
vary
Origin
server
cloudflare
GET
H2
200
Roobert-SemiBold-9d9c1ae0fc78f67d82c4fc43987857f5b897d29b903701d1e97c2e207311d636.woff2
assets.teepublic.com/assets/
30 KB
31 KB
192ms
47ms
Font
font/woff2
2a06:98c1:3103::6812:26a1
Cloudflare
General
Full URL
https://assets.teepublic.com/assets/Roobert-SemiBold-9d9c1ae0fc78f67d82c4fc43987857f5b897d29b903701d1e97c2e207311d636.woff2
Requested by
Host: erhassa.com
URL: https://erhassa.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a06:98c1:3103::6812:26a1 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
dc107e99a4239bb6051cfc228578a1b2355cba1ea9b6fff08bec097159bed0c3
Security Headers
Name Value
Strict-Transport-Security max-age=15768000; includeSubDomains; preload

Request headers

Origin
https://erhassa.com
sec-ch-ua-platform
"Linux"
Referer
https://erhassa.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=15768000; includeSubDomains; preload
cache-control
public, max-age=14400
timing-allow-origin
https://www.teepublic.com
content-encoding
gzip
cf-cache-status
HIT
etag
W/"ac259bfb34065e0f2655015e70bf650b"
age
4515
cf-ray
a383de02fd41fd3f-SIN
expires
Wed, 09 Sep 2026 09:42:01 GMT
access-control-allow-origin
*
date
Wed, 09 Sep 2026 05:42:01 GMT
content-type
font/woff2
last-modified
Mon, 17 Jul 2023 18:35:50 GMT
vary
Origin
server
cloudflare
GET
H2
200
Roobert-Bold-e95979b74ebe06c1851ece294f8f7e9e6d3ad0d817d1968dcbfb26373f0b4de5.woff2
assets.teepublic.com/assets/
30 KB
31 KB
169ms
25ms
Font
font/woff2
2a06:98c1:3103::6812:26a1
Cloudflare
General
Full URL
https://assets.teepublic.com/assets/Roobert-Bold-e95979b74ebe06c1851ece294f8f7e9e6d3ad0d817d1968dcbfb26373f0b4de5.woff2
Requested by
Host: erhassa.com
URL: https://erhassa.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a06:98c1:3103::6812:26a1 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
778709e9f6ce30c8159d616dcaf4e4a1a586bae98323efe7980fe08a1a8e98bb
Security Headers
Name Value
Strict-Transport-Security max-age=15768000; includeSubDomains; preload

Request headers

Origin
https://erhassa.com
sec-ch-ua-platform
"Linux"
Referer
https://erhassa.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=15768000; includeSubDomains; preload
cache-control
public, max-age=14400
timing-allow-origin
https://www.teepublic.com
content-encoding
gzip
cf-cache-status
HIT
etag
W/"a14dc388ed4cfd583e68e5740800bd88"
age
4515
cf-ray
a383de02fd45fd3f-SIN
expires
Wed, 09 Sep 2026 09:42:01 GMT
access-control-allow-origin
*
date
Wed, 09 Sep 2026 05:42:01 GMT
content-type
font/woff2
last-modified
Mon, 17 Jul 2023 18:35:46 GMT
vary
Origin
server
cloudflare
GET
H2
200
SharpGroteskBold-f0bacf6ef6410646205690dca3bc65f5bb2d31b9417a358ad9c07237a310d196.woff2
assets.teepublic.com/assets/
48 KB
49 KB
170ms
26ms
Font
font/woff2
2a06:98c1:3103::6812:26a1
Cloudflare
General
Full URL
https://assets.teepublic.com/assets/SharpGroteskBold-f0bacf6ef6410646205690dca3bc65f5bb2d31b9417a358ad9c07237a310d196.woff2
Requested by
Host: erhassa.com
URL: https://erhassa.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a06:98c1:3103::6812:26a1 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
b092b04d0f2c93375d3de1e2fe111af6706567d6abc1d7cfd8b57ad169a441cb
Security Headers
Name Value
Strict-Transport-Security max-age=15768000; includeSubDomains; preload

Request headers

Origin
https://erhassa.com
sec-ch-ua-platform
"Linux"
Referer
https://erhassa.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=15768000; includeSubDomains; preload
cache-control
public, max-age=14400
timing-allow-origin
https://www.teepublic.com
content-encoding
gzip
cf-cache-status
HIT
etag
W/"f5d71740edf2c05dc44ae87a7105a35d"
age
4515
cf-ray
a383de02fd3cfd3f-SIN
expires
Wed, 09 Sep 2026 09:42:01 GMT
access-control-allow-origin
*
date
Wed, 09 Sep 2026 05:42:01 GMT
content-type
font/woff2
last-modified
Mon, 17 Jul 2023 18:35:10 GMT
vary
Origin
server
cloudflare
GET
H2
200
logo-kangjitu.webp
gambar.caramel.in.net/uploads/KANGJITU/
4 KB
5 KB
146ms
4ms
Image
image/webp
167.99.66.65
DigitalOcean
General
Full URL
https://gambar.caramel.in.net/uploads/KANGJITU/logo-kangjitu.webp
Requested by
Host: erhassa.com
URL: https://erhassa.com/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
167.99.66.65 Singapore, Singapore, ASN14061 (DIGITALOCEAN-ASN - DigitalOcean, LLC, US),
Reverse DNS
Software
nginx /
Resource Hash
1259f54ed212e285e2788dc50877bf890e5e515628157c35d04bcd013b94d29d
Security Headers
Name Value
Strict-Transport-Security max-age=31536000

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://erhassa.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
etag
"6a8d1ee9-11d4"
accept-ranges
bytes
content-length
4564
date
Wed, 09 Sep 2026 05:42:01 GMT
content-type
image/webp
last-modified
Tue, 25 Aug 2026 04:49:45 GMT
server
nginx
GET
H2
200
kangjitu-icon-web.webp
gambar.caramel.in.net/uploads/KANGJITU/
1018 B
1 KB
12ms
2ms
Image
image/webp
167.99.66.65
DigitalOcean
General
Full URL
https://gambar.caramel.in.net/uploads/KANGJITU/kangjitu-icon-web.webp
Requested by
Host: erhassa.com
URL: https://erhassa.com/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
167.99.66.65 Singapore, Singapore, ASN14061 (DIGITALOCEAN-ASN - DigitalOcean, LLC, US),
Reverse DNS
Software
nginx /
Resource Hash
212c5ea5f38ddc6fdb73d6f759c919c20d7a310ed263443a476a5ac9ce3c6ff5
Security Headers
Name Value
Strict-Transport-Security max-age=31536000

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://erhassa.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
etag
"6a8d1ee9-3fa"
accept-ranges
bytes
content-length
1018
date
Wed, 09 Sep 2026 05:42:01 GMT
content-type
image/webp
last-modified
Tue, 25 Aug 2026 04:49:45 GMT
server
nginx
GET
H2
200
product_page-2af4d77ccb74974f4afec6972768b6abd2dca23b01d5b2e7380c8a38dff3c308.js Show response
assets.teepublic.com/assets/
132 KB
45 KB
170ms
32ms
Script
text/plain
2a06:98c1:3103::6812:26a1
Cloudflare
General
Full URL
https://assets.teepublic.com/assets/product_page-2af4d77ccb74974f4afec6972768b6abd2dca23b01d5b2e7380c8a38dff3c308.js
Requested by
Host: erhassa.com
URL: https://erhassa.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a06:98c1:3103::6812:26a1 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
42ae886e435b0859e06afe4c42a690eb6e988dcc5d689a4c82546f0ed6274e94
Security Headers
Name Value
Strict-Transport-Security max-age=15768000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://erhassa.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=15768000; includeSubDomains; preload
cache-control
public, max-age=14400
timing-allow-origin
https://www.teepublic.com
content-encoding
gzip
cf-cache-status
HIT
etag
W/"22c1d06ac910e869e5363cd82ca022b1"
age
77155
cf-ray
a383de02ee8b6014-SIN
expires
Wed, 09 Sep 2026 09:42:01 GMT
date
Wed, 09 Sep 2026 05:42:01 GMT
last-modified
Tue, 09 Sep 2025 18:40:19 GMT
server
cloudflare
GET
H2
200
product_page-c8d7a3eb618da10ad666.js Show response
assets.teepublic.com/packs/js/
384 KB
95 KB
90ms
51ms
Script
text/plain
2a06:98c1:3103::6812:26a1
Cloudflare
General
Full URL
https://assets.teepublic.com/packs/js/product_page-c8d7a3eb618da10ad666.js
Requested by
Host: erhassa.com
URL: https://erhassa.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a06:98c1:3103::6812:26a1 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
7ead77cf730b14f39e36d34bd0211644ce6e09fa8d90078b2b91a3eddd668c3b
Security Headers
Name Value
Strict-Transport-Security max-age=15768000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://erhassa.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=15768000; includeSubDomains; preload
cache-control
public, max-age=14400
timing-allow-origin
https://www.teepublic.com
content-encoding
gzip
cf-cache-status
HIT
etag
W/"e4cf7d6e6323932fe8be02882f5ecd5b"
age
74239
cf-ray
a383de036ef96014-SIN
expires
Wed, 09 Sep 2026 09:42:01 GMT
date
Wed, 09 Sep 2026 05:42:01 GMT
last-modified
Tue, 23 Sep 2025 19:26:18 GMT
server
cloudflare
GET
H2
200
js Show response
www.googletagmanager.com/gtag/
498 KB
168 KB
81ms
14ms
Script
application/javascript
2404:6800:4003:c11::61
Google LLC
General
Full URL
https://www.googletagmanager.com/gtag/js?id=G-404GXE7LR3
Requested by
Host: erhassa.com
URL: https://erhassa.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2404:6800:4003:c11::61 Singapore, Singapore, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
Google Tag Manager /
Resource Hash
3e63525c214d7d68ce1f129565ffe17758b4a608059eead6bbfa65900c7a4411
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://erhassa.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
private, max-age=900
content-encoding
zstd
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
expires
Wed, 09 Sep 2026 05:42:02 GMT
access-control-allow-origin
*
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
171873
date
Wed, 09 Sep 2026 05:42:02 GMT
x-xss-protection
0
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
server
Google Tag Manager
access-control-allow-headers
Cache-Control
GET
H3
200
badge Show response
www.google.com/shopping/customerreviews/ Frame 6563
38 KB
10 KB
1346ms
1250ms
Document
text/html
142.251.156.119
Google LLC
General
Full URL
https://www.google.com/shopping/customerreviews/badge?usegapi=1&merchant_id=107797987&position=INLINE&hl=en_US&origin=https%3A%2F%2Fwww.teepublic.com&gsrc=3p&jsh=m%3B%2F_%2Fscs%2Fabc-static%2F_%2Fjs%2Fk%3Dgapi.lb.en.8uXxGUoumbY.O%2Fd%3D1%2Frs%3DAHpOoo96qx3mL4tzGUOa-0q0udyPRqEAoA%2Fm%3D__features__
Requested by
Host: erhassa.com
URL: https://erhassa.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.156.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
3e5e01f850c7dc8042ad991990dfef7059ad69f624a1c2660ce9f9b51bd585e5
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script';report-uri /_/VerifiedReviewsBadgeUi/cspreport script-src 'report-sample' 'nonce-hSJsZldMUeSF1Kyshzv-vw' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/VerifiedReviewsBadgeUi/cspreport;worker-src 'self' script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/VerifiedReviewsBadgeUi/cspreport/allowlist
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://erhassa.com/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cache-control
private, max-age=900
content-encoding
gzip
content-security-policy
require-trusted-types-for 'script';report-uri /_/VerifiedReviewsBadgeUi/cspreport script-src 'report-sample' 'nonce-hSJsZldMUeSF1Kyshzv-vw' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/VerifiedReviewsBadgeUi/cspreport;worker-src 'self' script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/VerifiedReviewsBadgeUi/cspreport/allowlist
content-security-policy-report-only
script-src 'unsafe-inline' 'unsafe-eval' blob: data: https://www.gstatic.com/_/mss/boq-one-google/_/ https://www.gstatic.com/og/_/js/ https://apis.google.com/js/api.js https://apis.google.com/js/client.js https://www.googletagmanager.com/gtag/js https://www.google-analytics.com/analytics.js https://www.googletagmanager.com/gtag/destination https://www.google.com/_/scs/shopping-verified-reviews-static/_/js/k=boq-shopping-verified-reviews.VerifiedReviewsBadgeUi.en_US.51Z8JiXdZnc.2018.O/ https://apis.google.com/_/scs/abc-static/_/js/;report-uri /_/VerifiedReviewsBadgeUi/cspreport/fine-allowlist
content-type
text/html; charset=utf-8
cross-origin-opener-policy
same-origin
cross-origin-resource-policy
same-site
date
Wed, 09 Sep 2026 05:42:03 GMT
expires
Wed, 09 Sep 2026 05:42:03 GMT
p3p
CP="This is not a P3P policy! See g.co/p3phelp for more info."
permissions-policy
ch-ua-arch=*, ch-ua-bitness=*, ch-ua-full-version=*, ch-ua-full-version-list=*, ch-ua-model=*, ch-ua-wow64=*, ch-ua-form-factors=*, ch-ua-platform=*, ch-ua-platform-version=*
reporting-endpoints
default="/_/VerifiedReviewsBadgeUi/web-reports?context=eJzjytHikmLw05BicCuPYmm9eY51OhCXLDrP2gbEXUA8B4gNFS6xOgNxkcQV1hYg_lR1g1Wk-gbrt2JfNo4SXzaWt_5su3rC2X6q2LOf9LFnz__jwC7m6cjevsmZ_eZjZ_agKy7sSYWu7EI8HKsfN19lE_jw9Ot-RiWjpPzC-OKM_IKCzLz0stSizLTM1JSi1LLM1PLi0szi1CKgWLyRgZGZgYWxoZ6BcXyBAQDV50HF"
server
ESF
vary
Sec-Fetch-Dest, Sec-Fetch-Mode, Sec-Fetch-Site
x-content-type-options
nosniff
x-xss-protection
0
GET
H2
200
payment-methods-domestic-e3efe0cf0b9636c5ed76d563d87735104df12cf15afda7d20911d95bdbf6e360.png
assets.teepublic.com/assets/vendors/
16 KB
15 KB
26ms
23ms
Image
image/png
2a06:98c1:3103::6812:26a1
Cloudflare
General
Full URL
https://assets.teepublic.com/assets/vendors/payment-methods-domestic-e3efe0cf0b9636c5ed76d563d87735104df12cf15afda7d20911d95bdbf6e360.png
Requested by
Host: erhassa.com
URL: https://erhassa.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a06:98c1:3103::6812:26a1 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
3a851df453e952ce514b319769f4f2ad22e8a29ecb9e79d0dc4744f67f2b64fd
Security Headers
Name Value
Strict-Transport-Security max-age=15768000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://erhassa.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=15768000; includeSubDomains; preload
cache-control
public, max-age=14400
timing-allow-origin
https://www.teepublic.com
content-encoding
gzip
cf-cache-status
HIT
etag
W/"6444d31a8dc99df5dcf47f311e812a95"
age
2028
cf-ray
a383de072a026014-SIN
expires
Wed, 09 Sep 2026 09:42:02 GMT
date
Wed, 09 Sep 2026 05:42:02 GMT
content-type
image/png
last-modified
Tue, 16 Apr 2024 16:23:33 GMT
server
cloudflare
GET
H2
200
bbb-f6c79431393cee623e1d7db1c8d5623312fe5c7de4f48a47d04fb4b0c435c5c0.png
assets.teepublic.com/assets/vendors/
14 KB
14 KB
23ms
21ms
Image
image/png
2a06:98c1:3103::6812:26a1
Cloudflare
General
Full URL
https://assets.teepublic.com/assets/vendors/bbb-f6c79431393cee623e1d7db1c8d5623312fe5c7de4f48a47d04fb4b0c435c5c0.png
Requested by
Host: erhassa.com
URL: https://erhassa.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a06:98c1:3103::6812:26a1 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
fca5865f91816cc63055735f94fe21c137902804167f8f0e49230d87a04ac7dc
Security Headers
Name Value
Strict-Transport-Security max-age=15768000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://erhassa.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=15768000; includeSubDomains; preload
cache-control
public, max-age=14400
timing-allow-origin
https://www.teepublic.com
content-encoding
gzip
cf-cache-status
HIT
etag
W/"b3b882df60b41530f7fed52de95f1886"
age
1007
cf-ray
a383de072a056014-SIN
expires
Wed, 09 Sep 2026 09:42:02 GMT
date
Wed, 09 Sep 2026 05:42:02 GMT
content-type
image/png
last-modified
Tue, 16 Apr 2024 16:23:34 GMT
server
cloudflare
GET
H2
200
spinner-6b9b25aa9eee76bff953098ec9d520217d6ad4aae2870e1b2d766e9f35797647.svg
assets.teepublic.com/assets/icons/
694 B
474 B
29ms
18ms
Image
image/svg+xml
2a06:98c1:3103::6812:26a1
Cloudflare
General
Full URL
https://assets.teepublic.com/assets/icons/spinner-6b9b25aa9eee76bff953098ec9d520217d6ad4aae2870e1b2d766e9f35797647.svg
Requested by
Host: assets.teepublic.com
URL: https://assets.teepublic.com/assets/bundles/product-27efacddfffc4e9541c100011b9e0cf4258b53d4bd8386ac5e37135f3cd07974.css
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a06:98c1:3103::6812:26a1 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
80eac9665108a18e66b7754ffcae1c97eaa8b5516d680b596d290c8fd33260f4
Security Headers
Name Value
Strict-Transport-Security max-age=15768000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://assets.teepublic.com/assets/bundles/product-27efacddfffc4e9541c100011b9e0cf4258b53d4bd8386ac5e37135f3cd07974.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=15768000; includeSubDomains; preload
cache-control
public, max-age=14400
timing-allow-origin
https://www.teepublic.com
content-encoding
gzip
cf-cache-status
HIT
etag
W/"d63a68cc7a3ebc7c8583e1acb7126064"
age
75178
cf-ray
a383de078a766014-SIN
expires
Wed, 09 Sep 2026 09:42:02 GMT
date
Wed, 09 Sep 2026 05:42:02 GMT
content-type
image/svg+xml
last-modified
Tue, 16 Apr 2024 16:24:07 GMT
server
cloudflare
GET
H2
200
product_tshirt-cb1652b6222e426e923a6d65ab993d87583905c32c5fcebb5bfe56c60b1813d6.svg
assets.teepublic.com/assets/teepublicons/
2 KB
1 KB
31ms
20ms
Image
image/svg+xml
2a06:98c1:3103::6812:26a1
Cloudflare
General
Full URL
https://assets.teepublic.com/assets/teepublicons/product_tshirt-cb1652b6222e426e923a6d65ab993d87583905c32c5fcebb5bfe56c60b1813d6.svg
Requested by
Host: assets.teepublic.com
URL: https://assets.teepublic.com/assets/bundles/product-27efacddfffc4e9541c100011b9e0cf4258b53d4bd8386ac5e37135f3cd07974.css
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a06:98c1:3103::6812:26a1 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
50949ab80f64ce02a76695926bfa9fc49a10edc926f927908b534d8efd42db6c
Security Headers
Name Value
Strict-Transport-Security max-age=15768000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://assets.teepublic.com/assets/bundles/product-27efacddfffc4e9541c100011b9e0cf4258b53d4bd8386ac5e37135f3cd07974.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=15768000; includeSubDomains; preload
cache-control
public, max-age=14400
timing-allow-origin
https://www.teepublic.com
content-encoding
gzip
cf-cache-status
HIT
etag
W/"75c564f20cab186123b5c8e1f806bd53"
age
84030
cf-ray
a383de078a7a6014-SIN
expires
Wed, 09 Sep 2026 09:42:02 GMT
date
Wed, 09 Sep 2026 05:42:02 GMT
content-type
image/svg+xml
last-modified
Tue, 16 Apr 2024 16:26:34 GMT
vary
Accept-Encoding
server
cloudflare
GET
H2
200
product_shorts-125f62c45a99cf09b14c7398092a193029ace9c221fafc4999e13d2ef19608d1.svg
assets.teepublic.com/assets/teepublicons/
12 KB
5 KB
32ms
21ms
Image
image/svg+xml
2a06:98c1:3103::6812:26a1
Cloudflare
General
Full URL
https://assets.teepublic.com/assets/teepublicons/product_shorts-125f62c45a99cf09b14c7398092a193029ace9c221fafc4999e13d2ef19608d1.svg
Requested by
Host: assets.teepublic.com
URL: https://assets.teepublic.com/assets/bundles/product-27efacddfffc4e9541c100011b9e0cf4258b53d4bd8386ac5e37135f3cd07974.css
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a06:98c1:3103::6812:26a1 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
96598db6007ffda68026efb1c68800049c538747a82d87e8ee394c36ee40ee62
Security Headers
Name Value
Strict-Transport-Security max-age=15768000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://assets.teepublic.com/assets/bundles/product-27efacddfffc4e9541c100011b9e0cf4258b53d4bd8386ac5e37135f3cd07974.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=15768000; includeSubDomains; preload
cache-control
public, max-age=14400
timing-allow-origin
https://www.teepublic.com
content-encoding
gzip
cf-cache-status
HIT
etag
W/"830303113e7df2c28e47d51cfbc6348a"
age
80261
cf-ray
a383de078a826014-SIN
expires
Wed, 09 Sep 2026 09:42:02 GMT
date
Wed, 09 Sep 2026 05:42:02 GMT
content-type
image/svg+xml
last-modified
Mon, 04 Aug 2025 21:06:04 GMT
server
cloudflare
GET
H2
200
product_hoodie-ff8720b9b1a3bf7fcc0e61bf56cd699efaacb8db06ba20b83589338c20631dac.svg
assets.teepublic.com/assets/teepublicons/
4 KB
2 KB
32ms
22ms
Image
image/svg+xml
2a06:98c1:3103::6812:26a1
Cloudflare
General
Full URL
https://assets.teepublic.com/assets/teepublicons/product_hoodie-ff8720b9b1a3bf7fcc0e61bf56cd699efaacb8db06ba20b83589338c20631dac.svg
Requested by
Host: assets.teepublic.com
URL: https://assets.teepublic.com/assets/bundles/product-27efacddfffc4e9541c100011b9e0cf4258b53d4bd8386ac5e37135f3cd07974.css
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a06:98c1:3103::6812:26a1 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
4e6299640ff8b534bc90fc19548ca8caa977281c81797daa816a71127b633ccf
Security Headers
Name Value
Strict-Transport-Security max-age=15768000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://assets.teepublic.com/assets/bundles/product-27efacddfffc4e9541c100011b9e0cf4258b53d4bd8386ac5e37135f3cd07974.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=15768000; includeSubDomains; preload
cache-control
public, max-age=14400
timing-allow-origin
https://www.teepublic.com
content-encoding
gzip
cf-cache-status
HIT
etag
W/"9f438df7156d8b5e09e9465ddf87b7be"
age
64976
cf-ray
a383de078a856014-SIN
expires
Wed, 09 Sep 2026 09:42:02 GMT
date
Wed, 09 Sep 2026 05:42:02 GMT
content-type
image/svg+xml
last-modified
Tue, 16 Apr 2024 16:25:17 GMT
server
cloudflare
GET
H2
200
product_hat-25e12e229a7b3d8867e8e5cf36022cb3452c6ebf8f4876c1f50aee33cbcd2298.svg
assets.teepublic.com/assets/teepublicons/
4 KB
2 KB
32ms
22ms
Image
image/svg+xml
2a06:98c1:3103::6812:26a1
Cloudflare
General
Full URL
https://assets.teepublic.com/assets/teepublicons/product_hat-25e12e229a7b3d8867e8e5cf36022cb3452c6ebf8f4876c1f50aee33cbcd2298.svg
Requested by
Host: assets.teepublic.com
URL: https://assets.teepublic.com/assets/bundles/product-27efacddfffc4e9541c100011b9e0cf4258b53d4bd8386ac5e37135f3cd07974.css
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a06:98c1:3103::6812:26a1 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
7893f701fbf393784062d3239223e80c7f989c9d7f993092f2527f0bc6d4f267
Security Headers
Name Value
Strict-Transport-Security max-age=15768000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://assets.teepublic.com/assets/bundles/product-27efacddfffc4e9541c100011b9e0cf4258b53d4bd8386ac5e37135f3cd07974.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=15768000; includeSubDomains; preload
cache-control
public, max-age=14400
timing-allow-origin
https://www.teepublic.com
content-encoding
gzip
cf-cache-status
HIT
etag
W/"3e1a7206282d5340e4c78e58bac7559f"
age
81468
cf-ray
a383de078a886014-SIN
expires
Wed, 09 Sep 2026 09:42:02 GMT
date
Wed, 09 Sep 2026 05:42:02 GMT
content-type
image/svg+xml
last-modified
Wed, 12 Jun 2024 14:55:10 GMT
vary
Accept-Encoding
server
cloudflare
GET
H2
200
product_kids-627eccdf0f446db928c65490522cdf8e82ec18b6b75ade60ae4cf5ca4a467faf.svg
assets.teepublic.com/assets/teepublicons/
4 KB
2 KB
37ms
28ms
Image
image/svg+xml
2a06:98c1:3103::6812:26a1
Cloudflare
General
Full URL
https://assets.teepublic.com/assets/teepublicons/product_kids-627eccdf0f446db928c65490522cdf8e82ec18b6b75ade60ae4cf5ca4a467faf.svg
Requested by
Host: assets.teepublic.com
URL: https://assets.teepublic.com/assets/bundles/product-27efacddfffc4e9541c100011b9e0cf4258b53d4bd8386ac5e37135f3cd07974.css
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a06:98c1:3103::6812:26a1 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
2ff36965d5c0e93e09e6b3549e587a907f7ee7a3037a5ca783e29ccdd13acd82
Security Headers
Name Value
Strict-Transport-Security max-age=15768000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://assets.teepublic.com/assets/bundles/product-27efacddfffc4e9541c100011b9e0cf4258b53d4bd8386ac5e37135f3cd07974.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=15768000; includeSubDomains; preload
cache-control
public, max-age=14400
timing-allow-origin
https://www.teepublic.com
content-encoding
gzip
cf-cache-status
HIT
etag
W/"165d6a33fba368b85703bd04db563926"
age
156
cf-ray
a383de078a896014-SIN
expires
Wed, 09 Sep 2026 09:42:02 GMT
date
Wed, 09 Sep 2026 05:42:02 GMT
content-type
image/svg+xml
last-modified
Tue, 16 Apr 2024 16:25:28 GMT
server
cloudflare
GET
H2
200
product_sticker-f567d08da532a7eeb12cbd9ee166fd6eef3f9cdd31f44d8bece7413a0b500bf1.svg
assets.teepublic.com/assets/teepublicons/
2 KB
1 KB
36ms
27ms
Image
image/svg+xml
2a06:98c1:3103::6812:26a1
Cloudflare
General
Full URL
https://assets.teepublic.com/assets/teepublicons/product_sticker-f567d08da532a7eeb12cbd9ee166fd6eef3f9cdd31f44d8bece7413a0b500bf1.svg
Requested by
Host: assets.teepublic.com
URL: https://assets.teepublic.com/assets/bundles/product-27efacddfffc4e9541c100011b9e0cf4258b53d4bd8386ac5e37135f3cd07974.css
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a06:98c1:3103::6812:26a1 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
2fced7f256590dcdf737de4d59e6ec64403decb57fe8a10f46823e330bd847e7
Security Headers
Name Value
Strict-Transport-Security max-age=15768000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://assets.teepublic.com/assets/bundles/product-27efacddfffc4e9541c100011b9e0cf4258b53d4bd8386ac5e37135f3cd07974.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=15768000; includeSubDomains; preload
cache-control
public, max-age=14400
timing-allow-origin
https://www.teepublic.com
content-encoding
gzip
cf-cache-status
HIT
etag
W/"7d15daeb798035f74da4faa6c66cb0be"
age
3136
cf-ray
a383de078a8c6014-SIN
expires
Wed, 09 Sep 2026 09:42:02 GMT
date
Wed, 09 Sep 2026 05:42:02 GMT
content-type
image/svg+xml
last-modified
Tue, 16 Apr 2024 16:25:10 GMT
server
cloudflare
GET
H2
200
product_tank-ffbc7a9ecd19d0466706de291f7c41ea4c9b560f8519af06e6957b8eb586f628.svg
assets.teepublic.com/assets/teepublicons/
2 KB
1 KB
33ms
25ms
Image
image/svg+xml
2a06:98c1:3103::6812:26a1
Cloudflare
General
Full URL
https://assets.teepublic.com/assets/teepublicons/product_tank-ffbc7a9ecd19d0466706de291f7c41ea4c9b560f8519af06e6957b8eb586f628.svg
Requested by
Host: assets.teepublic.com
URL: https://assets.teepublic.com/assets/bundles/product-27efacddfffc4e9541c100011b9e0cf4258b53d4bd8386ac5e37135f3cd07974.css
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a06:98c1:3103::6812:26a1 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
8b386600aa0eb4c6398ee6f7f0f4040b53ec936b8aee73f27d0154a1ceb0379a
Security Headers
Name Value
Strict-Transport-Security max-age=15768000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://assets.teepublic.com/assets/bundles/product-27efacddfffc4e9541c100011b9e0cf4258b53d4bd8386ac5e37135f3cd07974.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=15768000; includeSubDomains; preload
cache-control
public, max-age=14400
timing-allow-origin
https://www.teepublic.com
content-encoding
gzip
cf-cache-status
HIT
etag
W/"6ae971706cdea122282c29f7d7a5c054"
age
447
cf-ray
a383de078a8d6014-SIN
expires
Wed, 09 Sep 2026 09:42:02 GMT
date
Wed, 09 Sep 2026 05:42:02 GMT
content-type
image/svg+xml
last-modified
Tue, 16 Apr 2024 16:25:36 GMT
server
cloudflare
GET
H2
200
product_mug-471b7ca6fa559ffc76b5e7ed09e2dcf62a0bd2c8a5cc560496778902b0e46483.svg
assets.teepublic.com/assets/teepublicons/
2 KB
1010 B
35ms
26ms
Image
image/svg+xml
2a06:98c1:3103::6812:26a1
Cloudflare
General
Full URL
https://assets.teepublic.com/assets/teepublicons/product_mug-471b7ca6fa559ffc76b5e7ed09e2dcf62a0bd2c8a5cc560496778902b0e46483.svg
Requested by
Host: assets.teepublic.com
URL: https://assets.teepublic.com/assets/bundles/product-27efacddfffc4e9541c100011b9e0cf4258b53d4bd8386ac5e37135f3cd07974.css
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a06:98c1:3103::6812:26a1 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
1d0c861ff2eeeac69e7cb798e5b03d59dcd95dd61b76d2daf316c08e3287d9d6
Security Headers
Name Value
Strict-Transport-Security max-age=15768000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://assets.teepublic.com/assets/bundles/product-27efacddfffc4e9541c100011b9e0cf4258b53d4bd8386ac5e37135f3cd07974.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=15768000; includeSubDomains; preload
cache-control
public, max-age=14400
timing-allow-origin
https://www.teepublic.com
content-encoding
gzip
cf-cache-status
HIT
etag
W/"938936a4ee706161454bd5aa438d24ce"
age
82032
cf-ray
a383de078a916014-SIN
expires
Wed, 09 Sep 2026 09:42:02 GMT
date
Wed, 09 Sep 2026 05:42:02 GMT
content-type
image/svg+xml
last-modified
Wed, 12 Jun 2024 14:55:10 GMT
server
cloudflare
GET
H2
200
globe_primary400-4459871cc25767dbb110c87407d9654283057ec0715e24b8bfb9e0f0aad7cfe9.svg
assets.teepublic.com/assets/teepublicons/
4 KB
2 KB
23ms
19ms
Image
image/svg+xml
2a06:98c1:3103::6812:26a1
Cloudflare
General
Full URL
https://assets.teepublic.com/assets/teepublicons/globe_primary400-4459871cc25767dbb110c87407d9654283057ec0715e24b8bfb9e0f0aad7cfe9.svg
Requested by
Host: erhassa.com
URL: https://erhassa.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a06:98c1:3103::6812:26a1 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
27d579a00be0c030f7b1abc77d60b8bc28332af49f86f047db384e0fb7d75b08
Security Headers
Name Value
Strict-Transport-Security max-age=15768000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://erhassa.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=15768000; includeSubDomains; preload
cache-control
public, max-age=14400
timing-allow-origin
https://www.teepublic.com
content-encoding
gzip
cf-cache-status
HIT
etag
W/"d6a219255d27d314892cfc350c89054b"
age
68682
cf-ray
a383de07ba9d6014-SIN
expires
Wed, 09 Sep 2026 09:42:02 GMT
date
Wed, 09 Sep 2026 05:42:02 GMT
content-type
image/svg+xml
last-modified
Mon, 22 Apr 2024 19:44:42 GMT
server
cloudflare
GET
H2
404
x_close_orange400-c1926221e50e7f6686d23ac344405449054e43f23d0f3306f15d8dfd546f999a.svg
assets.teepublic.com/assets/teepublicons/
27 KB
6 KB
328ms
325ms
Image
image/svg+xml
2a06:98c1:3103::6812:26a1
Cloudflare
General
Full URL
https://assets.teepublic.com/assets/teepublicons/x_close_orange400-c1926221e50e7f6686d23ac344405449054e43f23d0f3306f15d8dfd546f999a.svg
Requested by
Host: erhassa.com
URL: https://erhassa.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a06:98c1:3103::6812:26a1 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
62c1c0b235e26952857139537b65f8272026cd1c385c1bf6dba20481ee8a6619
Security Headers
Name Value
Strict-Transport-Security max-age=15768000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://erhassa.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=15768000; includeSubDomains; preload
cache-control
public, max-age=14400
timing-allow-origin
https://www.teepublic.com
content-encoding
gzip
cf-cache-status
EXPIRED
cf-ray
a383de07baa06014-SIN
expires
Wed, 09 Sep 2026 09:42:02 GMT
date
Wed, 09 Sep 2026 05:42:02 GMT
content-type
image/svg+xml
server
cloudflare
GET
H2
200
user_primary400-cbe4923027a0625a846acda949725368bbe52ac03f2bde950bf4891a338de0a5.svg
assets.teepublic.com/assets/teepublicons/
466 B
428 B
25ms
22ms
Image
image/svg+xml
2a06:98c1:3103::6812:26a1
Cloudflare
General
Full URL
https://assets.teepublic.com/assets/teepublicons/user_primary400-cbe4923027a0625a846acda949725368bbe52ac03f2bde950bf4891a338de0a5.svg
Requested by
Host: erhassa.com
URL: https://erhassa.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a06:98c1:3103::6812:26a1 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
717d0b286d5a89759167019ca1b0795dfc8c3801191d5d9f918aa9d12605324a
Security Headers
Name Value
Strict-Transport-Security max-age=15768000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://erhassa.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=15768000; includeSubDomains; preload
cache-control
public, max-age=14400
timing-allow-origin
https://www.teepublic.com
content-encoding
gzip
cf-cache-status
HIT
etag
W/"474e081a6931a10079e0e98bd149ef51"
age
68623
cf-ray
a383de07baa26014-SIN
expires
Wed, 09 Sep 2026 09:42:02 GMT
date
Wed, 09 Sep 2026 05:42:02 GMT
content-type
image/svg+xml
last-modified
Mon, 22 Apr 2024 19:44:44 GMT
server
cloudflare
POST
H2
204
collect
www.google-analytics.com/g/
0
0
253ms
7ms
Fetch
text/plain
2404:6800:4003:c01::65
Google LLC
General
Full URL
https://www.google-analytics.com/g/collect?v=2&tid=G-404GXE7LR3&gtm=45je6930v9228059991za200zd9228059991&_p=1788932522287&gcd=13l3l3l3l1l1&npa=0&dma=0&cid=278507790.1788932523&frm=0&ngs=1&pscdl=noapi&rcb=6&sr=1600x1200&uaa=x86&uab=64&uafvl=Chromium%3B152.0.7977.82%7CGoogle%2520Chrome%3B152.0.7977.82%7CNot%253FA_Brand%3B24.0.0.0&uam=&uamb=0&uap=Linux&uapv=&uaw=0&ul=en-sg&_s=1&tag_exp=115938466~115938469~118897920~118897930~120213116~120385423~120469145~120469153~120914214&sid=1788932522&sct=1&seg=0&dl=https%3A%2F%2Ferhassa.com%2F&dt=Paito%20Toto%20Macau%204D%2C%20Data%20%26%20Keluaran%20Toto%20Macau%20Terbaru%20Result%20Akurat%20%7C%20KANGJITU&en=page_view&_fv=1&_nsi=1&_ss=1&_ee=1&tfd=1429
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtag/js?id=G-404GXE7LR3
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2404:6800:4003:c01::65 Singapore, Singapore, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
Golfe2 /
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://erhassa.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, no-store, must-revalidate
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
content-security-policy-report-only
script-src 'none'; form-action 'none'; frame-src 'none'; report-uri https://csp.withgoogle.com/csp/scaffolding/ascnsrsggc:139:0
report-to
{"group":"ascnsrsggc:139:0","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/scaffolding/ascnsrsggc:139:0"}],}
expires
Fri, 01 Jan 1990 00:00:00 GMT
access-control-allow-origin
https://erhassa.com
cross-origin-opener-policy-report-only
same-origin; report-to=ascnsrsggc:139:0
content-length
0
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 09 Sep 2026 05:42:02 GMT
content-type
text/plain
server
Golfe2
GET
H3
200
m=_b,_tp Show response
www.google.com/_/scs/shopping-verified-reviews-static/_/js/k=boq-shopping-verified-reviews.VerifiedReviewsBadgeUi.en_US.51Z8JiXdZnc.2018.O/am=AAAAADQ/d=1/excm=_b,_tp,badgeview/ed=1/dg=0/wt=2/ujg=1/... Frame 6563
149 KB
55 KB
23ms
15ms
Script
text/javascript
142.251.156.119
Google LLC
General
Full URL
https://www.google.com/_/scs/shopping-verified-reviews-static/_/js/k=boq-shopping-verified-reviews.VerifiedReviewsBadgeUi.en_US.51Z8JiXdZnc.2018.O/am=AAAAADQ/d=1/excm=_b,_tp,badgeview/ed=1/dg=0/wt=2/ujg=1/rs=AC8lLkSTGbA82BrEvKI_BPRQ5XbgFgk2Pg/dti=1/m=_b,_tp
Requested by
Host: www.google.com
URL: https://www.google.com/shopping/customerreviews/badge?usegapi=1&merchant_id=107797987&position=INLINE&hl=en_US&origin=https%3A%2F%2Fwww.teepublic.com&gsrc=3p&jsh=m%3B%2F_%2Fscs%2Fabc-static%2F_%2Fjs%2Fk%3Dgapi.lb.en.8uXxGUoumbY.O%2Fd%3D1%2Frs%3DAHpOoo96qx3mL4tzGUOa-0q0udyPRqEAoA%2Fm%3D__features__
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.156.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
dbb92e32cb1a4c797c36c457f42e9a9b95998f659c02cec2a3f524a7ba34b0d6
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.google.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
age
232882
report-to
{"group":"boq-infra/shopping-verified-reviews-boq-js-css-signers","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/boq-infra/shopping-verified-reviews-boq-js-css-signers"}]}
x-content-type-options
nosniff
expires
Mon, 06 Sep 2027 13:00:41 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sun, 06 Sep 2026 13:00:41 GMT
last-modified
Mon, 31 Aug 2026 09:58:35 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
cache-control
public, immutable, max-age=31536000
cross-origin-opener-policy
same-origin; report-to="boq-infra/shopping-verified-reviews-boq-js-css-signers"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/boq-infra/shopping-verified-reviews-boq-js-css-signers
accept-ranges
bytes
content-length
56523
x-xss-protection
0
server
sffe
GET
H2
200
js Show response
www.googletagmanager.com/gtag/ Frame 6563
507 KB
170 KB
40ms
8ms
Script
application/javascript
2404:6800:4003:c11::61
Google LLC
General
Full URL
https://www.googletagmanager.com/gtag/js?id=G-2M8CLPGL2R
Requested by
Host: www.google.com
URL: https://www.google.com/shopping/customerreviews/badge?usegapi=1&merchant_id=107797987&position=INLINE&hl=en_US&origin=https%3A%2F%2Fwww.teepublic.com&gsrc=3p&jsh=m%3B%2F_%2Fscs%2Fabc-static%2F_%2Fjs%2Fk%3Dgapi.lb.en.8uXxGUoumbY.O%2Fd%3D1%2Frs%3DAHpOoo96qx3mL4tzGUOa-0q0udyPRqEAoA%2Fm%3D__features__
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2404:6800:4003:c11::61 Singapore, Singapore, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
Google Tag Manager /
Resource Hash
5ba0c95dc25e92dbd022b6fafd63bcc555056e24ec19d4c0a7a51cf61f52ff24
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.google.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
private, max-age=900
content-encoding
zstd
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
expires
Wed, 09 Sep 2026 05:42:03 GMT
access-control-allow-origin
*
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
173953
date
Wed, 09 Sep 2026 05:42:03 GMT
x-xss-protection
0
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
server
Google Tag Manager
access-control-allow-headers
Cache-Control
GET
H3
200
gray_stars_large.png
www.gstatic.com/verifiedreviews/ Frame 6563
943 B
966 B
24ms
17ms
Image
image/png
142.251.156.119
Google LLC
General
Full URL
https://www.gstatic.com/verifiedreviews/gray_stars_large.png
Requested by
Host: www.google.com
URL: https://www.google.com/shopping/customerreviews/badge?usegapi=1&merchant_id=107797987&position=INLINE&hl=en_US&origin=https%3A%2F%2Fwww.teepublic.com&gsrc=3p&jsh=m%3B%2F_%2Fscs%2Fabc-static%2F_%2Fjs%2Fk%3Dgapi.lb.en.8uXxGUoumbY.O%2Fd%3D1%2Frs%3DAHpOoo96qx3mL4tzGUOa-0q0udyPRqEAoA%2Fm%3D__features__
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.156.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
fd4188121a6c9b28d029ebc07cd1db2f35e0657b4a2e825f901ed8b2b37bb327
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.google.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
public, max-age=31536000
age
470726
cross-origin-resource-policy
cross-origin
report-to
{"group":"static-on-bigtable","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/static-on-bigtable"}]}
x-content-type-options
nosniff
expires
Fri, 03 Sep 2027 18:56:37 GMT
accept-ranges
bytes
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cross-origin-opener-policy-report-only
same-origin; report-to="static-on-bigtable"
content-length
943
x-xss-protection
0
date
Thu, 03 Sep 2026 18:56:37 GMT
last-modified
Thu, 03 Oct 2019 10:15:00 GMT
content-type
image/png
server
sffe
GET
H3
200
orange_stars_large.png
www.gstatic.com/verifiedreviews/ Frame 6563
945 B
968 B
22ms
15ms
Image
image/png
142.251.156.119
Google LLC
General
Full URL
https://www.gstatic.com/verifiedreviews/orange_stars_large.png
Requested by
Host: www.google.com
URL: https://www.google.com/shopping/customerreviews/badge?usegapi=1&merchant_id=107797987&position=INLINE&hl=en_US&origin=https%3A%2F%2Fwww.teepublic.com&gsrc=3p&jsh=m%3B%2F_%2Fscs%2Fabc-static%2F_%2Fjs%2Fk%3Dgapi.lb.en.8uXxGUoumbY.O%2Fd%3D1%2Frs%3DAHpOoo96qx3mL4tzGUOa-0q0udyPRqEAoA%2Fm%3D__features__
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.156.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
a8703732fc112fb61adbc3715a19ebc0944a5544c64ee314ade6140ec57ec644
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.google.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
public, max-age=31536000
age
380912
cross-origin-resource-policy
cross-origin
report-to
{"group":"static-on-bigtable","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/static-on-bigtable"}]}
x-content-type-options
nosniff
expires
Sat, 04 Sep 2027 19:53:31 GMT
accept-ranges
bytes
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cross-origin-opener-policy-report-only
same-origin; report-to="static-on-bigtable"
content-length
945
x-xss-protection
0
date
Fri, 04 Sep 2026 19:53:31 GMT
last-modified
Thu, 03 Oct 2019 10:15:00 GMT
content-type
image/png
server
sffe
GET
H3
200
gcr_logo_stacked.png
www.gstatic.com/verifiedreviews/en/ Frame 6563
1 KB
1 KB
23ms
16ms
Image
image/png
142.251.156.119
Google LLC
General
Full URL
https://www.gstatic.com/verifiedreviews/en/gcr_logo_stacked.png
Requested by
Host: www.google.com
URL: https://www.google.com/shopping/customerreviews/badge?usegapi=1&merchant_id=107797987&position=INLINE&hl=en_US&origin=https%3A%2F%2Fwww.teepublic.com&gsrc=3p&jsh=m%3B%2F_%2Fscs%2Fabc-static%2F_%2Fjs%2Fk%3Dgapi.lb.en.8uXxGUoumbY.O%2Fd%3D1%2Frs%3DAHpOoo96qx3mL4tzGUOa-0q0udyPRqEAoA%2Fm%3D__features__
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.156.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
ab8debe19f138dd26978779dceefc172902368b4cb943bc09d14fa6c01a6e322
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.google.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

cache-control
public, max-age=31536000
age
470726
cross-origin-resource-policy
cross-origin
report-to
{"group":"static-on-bigtable","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/static-on-bigtable"}]}
x-content-type-options
nosniff
expires
Fri, 03 Sep 2027 18:56:37 GMT
accept-ranges
bytes
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cross-origin-opener-policy-report-only
same-origin; report-to="static-on-bigtable"
content-length
1499
x-xss-protection
0
date
Thu, 03 Sep 2026 18:56:37 GMT
last-modified
Thu, 03 Oct 2019 10:15:00 GMT
content-type
image/png
server
sffe
GET
H3
200
m=vhDjqd Show response
www.google.com/_/scs/shopping-verified-reviews-static/_/js/k=boq-shopping-verified-reviews.VerifiedReviewsBadgeUi.en_US.51Z8JiXdZnc.2018.O/ck=boq-shopping-verified-reviews.VerifiedReviewsBadgeUi.sB... Frame 6563
117 KB
43 KB
13ms
12ms
Script
text/javascript
142.251.156.119
Google LLC
General
Full URL
https://www.google.com/_/scs/shopping-verified-reviews-static/_/js/k=boq-shopping-verified-reviews.VerifiedReviewsBadgeUi.en_US.51Z8JiXdZnc.2018.O/ck=boq-shopping-verified-reviews.VerifiedReviewsBadgeUi.sBSJf4mDfCo.L.B1.O/am=AAAAADQ/d=1/exm=_b,_tp/excm=_b,_tp,badgeview/ed=1/wt=2/ujg=1/rs=AC8lLkQDtznnSSJH6ZnRCE2tMj-EcnGzUg/ee=EmZ2Bf:zr1jrb;JsbNhc:Xd8iUd;K5nYTd:ZDZcre;LBgRLc:XVMNvd;Me32dd:MEeYgc;NJ1rfe:yGfSdd;NPKaK:PVlQOd;Pjplud:EEDORb;QGR0gd:Mlhmy;SNUn3:ZwDk9d;ScI3Yc:e7Hzgb;Uvc8o:VDovNc;YIZmRd:A1yn5d;a56pNe:JEfCwb;cEt90b:ws9Tlc;dIoSBb:SpsfSb;dowIGb:ebZ3mb;eBAeSb:zbML3c;iFQyKf:vfuNJf;lOO0Vd:OTA3Ae;oGtAuc:sOXFj;qQEoOc:KUM7Z;qafBPd:yDVVkb;qddgKe:xQtZb;wR5FRb:siKnQd;yxTchf:KUM7Z/dti=1/m=vhDjqd
Requested by
Host: www.google.com
URL: https://www.google.com/_/scs/shopping-verified-reviews-static/_/js/k=boq-shopping-verified-reviews.VerifiedReviewsBadgeUi.en_US.51Z8JiXdZnc.2018.O/am=AAAAADQ/d=1/excm=_b,_tp,badgeview/ed=1/dg=0/wt=2/ujg=1/rs=AC8lLkSTGbA82BrEvKI_BPRQ5XbgFgk2Pg/dti=1/m=_b,_tp
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.156.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
63d5c76fcaa2c2a630aec6fac234d7a7b659605280e89cb98b92ee088fb5765d
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.google.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
age
253521
report-to
{"group":"boq-infra/shopping-verified-reviews-boq-js-css-signers","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/boq-infra/shopping-verified-reviews-boq-js-css-signers"}]}
x-content-type-options
nosniff
expires
Mon, 06 Sep 2027 07:16:42 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sun, 06 Sep 2026 07:16:42 GMT
last-modified
Tue, 18 Aug 2026 21:58:16 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
cache-control
public, immutable, max-age=31536000
cross-origin-opener-policy
same-origin; report-to="boq-infra/shopping-verified-reviews-boq-js-css-signers"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/boq-infra/shopping-verified-reviews-boq-js-css-signers
accept-ranges
bytes
content-length
43517
x-xss-protection
0
server
sffe
GET
H2
200
api.js Show response
apis.google.com/js/ Frame 6563
14 KB
6 KB
53ms
11ms
Script
text/javascript
2404:6800:4003:c11::8b
Google LLC
General
Full URL
https://apis.google.com/js/api.js
Requested by
Host: www.google.com
URL: https://www.google.com/_/scs/shopping-verified-reviews-static/_/js/k=boq-shopping-verified-reviews.VerifiedReviewsBadgeUi.en_US.51Z8JiXdZnc.2018.O/ck=boq-shopping-verified-reviews.VerifiedReviewsBadgeUi.sBSJf4mDfCo.L.B1.O/am=AAAAADQ/d=1/exm=_b,_tp/excm=_b,_tp,badgeview/ed=1/wt=2/ujg=1/rs=AC8lLkQDtznnSSJH6ZnRCE2tMj-EcnGzUg/ee=EmZ2Bf:zr1jrb;JsbNhc:Xd8iUd;K5nYTd:ZDZcre;LBgRLc:XVMNvd;Me32dd:MEeYgc;NJ1rfe:yGfSdd;NPKaK:PVlQOd;Pjplud:EEDORb;QGR0gd:Mlhmy;SNUn3:ZwDk9d;ScI3Yc:e7Hzgb;Uvc8o:VDovNc;YIZmRd:A1yn5d;a56pNe:JEfCwb;cEt90b:ws9Tlc;dIoSBb:SpsfSb;dowIGb:ebZ3mb;eBAeSb:zbML3c;iFQyKf:vfuNJf;lOO0Vd:OTA3Ae;oGtAuc:sOXFj;qQEoOc:KUM7Z;qafBPd:yDVVkb;qddgKe:xQtZb;wR5FRb:siKnQd;yxTchf:KUM7Z/dti=1/m=vhDjqd
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2404:6800:4003:c11::8b Singapore, Singapore, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
cd74472112978d7bafee49927769110f6f619373105d7f408add04b4098861cd
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/gapi-team
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.google.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
"2deffdf3986fdbe0"
report-to
{"group":"gapi-team","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/gapi-team"}]}
x-content-type-options
nosniff
expires
Wed, 09 Sep 2026 05:42:03 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 09 Sep 2026 05:42:03 GMT
content-type
text/javascript
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/gapi-team
cache-control
private, max-age=1800, stale-while-revalidate=1800
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="gapi-team"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
content-length
5866
x-xss-protection
0
server
sffe
GET
H2
200
cb=gapi.loaded_0 Show response
apis.google.com/_/scs/abc-static/_/js/k=gapi.lb.en.8uXxGUoumbY.O/m=gapi_iframes,gapi_iframes_style_common/rt=j/sv=1/d=1/ed=1/rs=AHpOoo96qx3mL4tzGUOa-0q0udyPRqEAoA/ Frame 6563
134 KB
45 KB
7ms
6ms
Script
text/javascript
2404:6800:4003:c11::8b
Google LLC
General
Full URL
https://apis.google.com/_/scs/abc-static/_/js/k=gapi.lb.en.8uXxGUoumbY.O/m=gapi_iframes,gapi_iframes_style_common/rt=j/sv=1/d=1/ed=1/rs=AHpOoo96qx3mL4tzGUOa-0q0udyPRqEAoA/cb=gapi.loaded_0?le=scs,fedcm_migration_mod
Requested by
Host: apis.google.com
URL: https://apis.google.com/js/api.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2404:6800:4003:c11::8b Singapore, Singapore, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
22494eb4f5fc2ef8c229b9df2e171990687e4837282655145cca0fa302af1278
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.google.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
age
499727
report-to
{"group":"social-frontend-mpm-access","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/social-frontend-mpm-access"}]}
x-content-type-options
nosniff
expires
Fri, 03 Sep 2027 10:53:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 03 Sep 2026 10:53:16 GMT
last-modified
Fri, 02 Feb 2024 17:51:09 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
cache-control
public, max-age=31536000
cross-origin-opener-policy
same-origin; report-to="social-frontend-mpm-access"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/social-frontend-mpm-access
accept-ranges
bytes
access-control-allow-origin
*
content-length
45690
x-xss-protection
0
server
sffe
GET
H2
200
product_page_non_critical-b3c32616b74cc64a463d89f471cc5f8ab832c96195372ee2960a820a2e3fd0a3.js Show response
assets.teepublic.com/assets/
10 KB
3 KB
22ms
20ms
Script
text/plain
2a06:98c1:3103::6812:26a1
Cloudflare
General
Full URL
https://assets.teepublic.com/assets/product_page_non_critical-b3c32616b74cc64a463d89f471cc5f8ab832c96195372ee2960a820a2e3fd0a3.js
Requested by
Host: assets.teepublic.com
URL: https://assets.teepublic.com/packs/js/product_page-c8d7a3eb618da10ad666.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a06:98c1:3103::6812:26a1 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
9684a25158374abc18c783c542321b64004bbd276157c159792dd929ebb87d5b
Security Headers
Name Value
Strict-Transport-Security max-age=15768000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://erhassa.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=15768000; includeSubDomains; preload
cache-control
public, max-age=14400
timing-allow-origin
https://www.teepublic.com
content-encoding
gzip
cf-cache-status
HIT
etag
W/"40b71d9413bda2f7a018cb2bdfab8a84"
age
83676
cf-ray
a383de135c516014-SIN
expires
Wed, 09 Sep 2026 09:42:04 GMT
date
Wed, 09 Sep 2026 05:42:04 GMT
last-modified
Tue, 19 Aug 2025 18:52:52 GMT
server
cloudflare
GET
H3
200
m=Wt6vjf,hhhU8,FCpbqb,WhJNk Show response
www.google.com/_/scs/shopping-verified-reviews-static/_/js/k=boq-shopping-verified-reviews.VerifiedReviewsBadgeUi.en_US.51Z8JiXdZnc.2018.O/ck=boq-shopping-verified-reviews.VerifiedReviewsBadgeUi.sB... Frame 6563
5 KB
2 KB
5ms
4ms
Script
text/javascript
142.251.156.119
Google LLC
General
Full URL
https://www.google.com/_/scs/shopping-verified-reviews-static/_/js/k=boq-shopping-verified-reviews.VerifiedReviewsBadgeUi.en_US.51Z8JiXdZnc.2018.O/ck=boq-shopping-verified-reviews.VerifiedReviewsBadgeUi.sBSJf4mDfCo.L.B1.O/am=AAAAADQ/d=1/exm=_b,_tp,vhDjqd/excm=_b,_tp,badgeview/ed=1/wt=2/ujg=1/rs=AC8lLkQDtznnSSJH6ZnRCE2tMj-EcnGzUg/ee=EmZ2Bf:zr1jrb;JsbNhc:Xd8iUd;K5nYTd:ZDZcre;LBgRLc:XVMNvd;Me32dd:MEeYgc;NJ1rfe:yGfSdd;NPKaK:PVlQOd;Pjplud:EEDORb;QGR0gd:Mlhmy;SNUn3:ZwDk9d;ScI3Yc:e7Hzgb;Uvc8o:VDovNc;YIZmRd:A1yn5d;a56pNe:JEfCwb;cEt90b:ws9Tlc;dIoSBb:SpsfSb;dowIGb:ebZ3mb;eBAeSb:zbML3c;iFQyKf:vfuNJf;lOO0Vd:OTA3Ae;oGtAuc:sOXFj;qQEoOc:KUM7Z;qafBPd:yDVVkb;qddgKe:xQtZb;wR5FRb:siKnQd;yxTchf:KUM7Z/dti=1/m=Wt6vjf,hhhU8,FCpbqb,WhJNk
Requested by
Host: www.google.com
URL: https://www.google.com/_/scs/shopping-verified-reviews-static/_/js/k=boq-shopping-verified-reviews.VerifiedReviewsBadgeUi.en_US.51Z8JiXdZnc.2018.O/am=AAAAADQ/d=1/excm=_b,_tp,badgeview/ed=1/dg=0/wt=2/ujg=1/rs=AC8lLkSTGbA82BrEvKI_BPRQ5XbgFgk2Pg/dti=1/m=_b,_tp
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.156.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
6e2b26a8cd7d2009b9fcf9a29d1d700763d4c8137ce364e63d27527b8f50c2e7
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.google.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
age
47387
report-to
{"group":"boq-infra/shopping-verified-reviews-boq-js-css-signers","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/boq-infra/shopping-verified-reviews-boq-js-css-signers"}]}
x-content-type-options
nosniff
expires
Wed, 08 Sep 2027 16:32:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Tue, 08 Sep 2026 16:32:17 GMT
last-modified
Tue, 18 Aug 2026 21:58:16 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
cache-control
public, immutable, max-age=31536000
cross-origin-opener-policy
same-origin; report-to="boq-infra/shopping-verified-reviews-boq-js-css-signers"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/boq-infra/shopping-verified-reviews-boq-js-css-signers
accept-ranges
bytes
content-length
2383
x-xss-protection
0
server
sffe
GET
H3
200
m=lwddkf,EFQ78c Show response
www.google.com/_/scs/shopping-verified-reviews-static/_/js/k=boq-shopping-verified-reviews.VerifiedReviewsBadgeUi.en_US.51Z8JiXdZnc.2018.O/ck=boq-shopping-verified-reviews.VerifiedReviewsBadgeUi.sB... Frame 6563
6 KB
2 KB
7ms
6ms
Script
text/javascript
142.251.156.119
Google LLC
General
Full URL
https://www.google.com/_/scs/shopping-verified-reviews-static/_/js/k=boq-shopping-verified-reviews.VerifiedReviewsBadgeUi.en_US.51Z8JiXdZnc.2018.O/ck=boq-shopping-verified-reviews.VerifiedReviewsBadgeUi.sBSJf4mDfCo.L.B1.O/am=AAAAADQ/d=1/exm=FCpbqb,WhJNk,Wt6vjf,_b,_tp,hhhU8,vhDjqd/excm=_b,_tp,badgeview/ed=1/wt=2/ujg=1/rs=AC8lLkQDtznnSSJH6ZnRCE2tMj-EcnGzUg/ee=EmZ2Bf:zr1jrb;JsbNhc:Xd8iUd;K5nYTd:ZDZcre;LBgRLc:XVMNvd;Me32dd:MEeYgc;NJ1rfe:yGfSdd;NPKaK:PVlQOd;Pjplud:EEDORb;QGR0gd:Mlhmy;SNUn3:ZwDk9d;ScI3Yc:e7Hzgb;Uvc8o:VDovNc;YIZmRd:A1yn5d;a56pNe:JEfCwb;cEt90b:ws9Tlc;dIoSBb:SpsfSb;dowIGb:ebZ3mb;eBAeSb:zbML3c;iFQyKf:vfuNJf;lOO0Vd:OTA3Ae;oGtAuc:sOXFj;qQEoOc:KUM7Z;qafBPd:yDVVkb;qddgKe:xQtZb;wR5FRb:siKnQd;yxTchf:KUM7Z/dti=1/m=lwddkf,EFQ78c
Requested by
Host: www.google.com
URL: https://www.google.com/_/scs/shopping-verified-reviews-static/_/js/k=boq-shopping-verified-reviews.VerifiedReviewsBadgeUi.en_US.51Z8JiXdZnc.2018.O/am=AAAAADQ/d=1/excm=_b,_tp,badgeview/ed=1/dg=0/wt=2/ujg=1/rs=AC8lLkSTGbA82BrEvKI_BPRQ5XbgFgk2Pg/dti=1/m=_b,_tp
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.156.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
1b364e96bbea76d041688d12226ed12a83de069f78ed930f224b94f87da35dcb
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.google.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
age
47387
report-to
{"group":"boq-infra/shopping-verified-reviews-boq-js-css-signers","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/boq-infra/shopping-verified-reviews-boq-js-css-signers"}]}
x-content-type-options
nosniff
expires
Wed, 08 Sep 2027 16:32:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Tue, 08 Sep 2026 16:32:17 GMT
last-modified
Tue, 18 Aug 2026 21:58:16 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
cache-control
public, immutable, max-age=31536000
cross-origin-opener-policy
same-origin; report-to="boq-infra/shopping-verified-reviews-boq-js-css-signers"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/boq-infra/shopping-verified-reviews-boq-js-css-signers
accept-ranges
bytes
content-length
2480
x-xss-protection
0
server
sffe
GET
H3
200
m=p3hmRc,LvGhrf,RqjULd Show response
www.google.com/_/scs/shopping-verified-reviews-static/_/js/k=boq-shopping-verified-reviews.VerifiedReviewsBadgeUi.en_US.51Z8JiXdZnc.2018.O/ck=boq-shopping-verified-reviews.VerifiedReviewsBadgeUi.sB... Frame 6563
40 KB
15 KB
9ms
9ms
Script
text/javascript
142.251.156.119
Google LLC
General
Full URL
https://www.google.com/_/scs/shopping-verified-reviews-static/_/js/k=boq-shopping-verified-reviews.VerifiedReviewsBadgeUi.en_US.51Z8JiXdZnc.2018.O/ck=boq-shopping-verified-reviews.VerifiedReviewsBadgeUi.sBSJf4mDfCo.L.B1.O/am=AAAAADQ/d=1/exm=EFQ78c,FCpbqb,WhJNk,Wt6vjf,_b,_tp,hhhU8,lwddkf,vhDjqd/excm=_b,_tp,badgeview/ed=1/wt=2/ujg=1/rs=AC8lLkQDtznnSSJH6ZnRCE2tMj-EcnGzUg/ee=EmZ2Bf:zr1jrb;JsbNhc:Xd8iUd;K5nYTd:ZDZcre;LBgRLc:XVMNvd;Me32dd:MEeYgc;NJ1rfe:yGfSdd;NPKaK:PVlQOd;Pjplud:EEDORb;QGR0gd:Mlhmy;SNUn3:ZwDk9d;ScI3Yc:e7Hzgb;Uvc8o:VDovNc;YIZmRd:A1yn5d;a56pNe:JEfCwb;cEt90b:ws9Tlc;dIoSBb:SpsfSb;dowIGb:ebZ3mb;eBAeSb:zbML3c;iFQyKf:vfuNJf;lOO0Vd:OTA3Ae;oGtAuc:sOXFj;qQEoOc:KUM7Z;qafBPd:yDVVkb;qddgKe:xQtZb;wR5FRb:siKnQd;yxTchf:KUM7Z/dti=1/m=p3hmRc,LvGhrf,RqjULd
Requested by
Host: www.google.com
URL: https://www.google.com/_/scs/shopping-verified-reviews-static/_/js/k=boq-shopping-verified-reviews.VerifiedReviewsBadgeUi.en_US.51Z8JiXdZnc.2018.O/am=AAAAADQ/d=1/excm=_b,_tp,badgeview/ed=1/dg=0/wt=2/ujg=1/rs=AC8lLkSTGbA82BrEvKI_BPRQ5XbgFgk2Pg/dti=1/m=_b,_tp
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.156.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
5ef586c8d4926e5c28868fb586be9160e68906b7385a8a7bc7ec04506a66fedf
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.google.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
age
421455
report-to
{"group":"boq-infra/shopping-verified-reviews-boq-js-css-signers","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/boq-infra/shopping-verified-reviews-boq-js-css-signers"}]}
x-content-type-options
nosniff
expires
Sat, 04 Sep 2027 08:37:49 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 04 Sep 2026 08:37:49 GMT
last-modified
Tue, 18 Aug 2026 21:58:16 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
cache-control
public, immutable, max-age=31536000
cross-origin-opener-policy
same-origin; report-to="boq-infra/shopping-verified-reviews-boq-js-css-signers"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/boq-infra/shopping-verified-reviews-boq-js-css-signers
accept-ranges
bytes
content-length
15595
x-xss-protection
0
server
sffe
GET
H2
200
kangjitu-icon-web.webp
gambar.caramel.in.net/uploads/KANGJITU/
1018 B
0
5ms
5ms
Other
image/webp
167.99.66.65
DigitalOcean
General
Full URL
https://gambar.caramel.in.net/uploads/KANGJITU/kangjitu-icon-web.webp
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
167.99.66.65 Singapore, Singapore, ASN14061 (DIGITALOCEAN-ASN - DigitalOcean, LLC, US),
Reverse DNS
Software
nginx /
Resource Hash
212c5ea5f38ddc6fdb73d6f759c919c20d7a310ed263443a476a5ac9ce3c6ff5

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://erhassa.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/152.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="152", "Google Chrome";v="152", "Not?A_Brand";v="24"
sec-ch-ua-mobile
?0

Response headers

accept-ranges
bytes
content-length
1018
date
Wed, 09 Sep 2026 05:42:01 GMT
etag
"6a8d1ee9-3fa"
content-type
image/webp
last-modified
Tue, 25 Aug 2026 04:49:45 GMT
server
nginx

Verdicts & Comments Add Verdict or Comment

15 JavaScript Window variables

These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.

object| 0 object| dataLayer object| TeePublic object| Cart function| $ function| jQuery object| jQuery112403115613648567689 function| Cookies function| setImmediate function| clearImmediate function| gtag object| google_tag_data object| google_tag_manager function| onYouTubeIframeAPIReady object| gaGlobal

4 Cookies

Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.

Domain/Path Expires Name / Value
.teepublic.com/ 1970-01-21
16:55:34
Name: __cf_bm
Value: vsbykIPH1bOcNdCzgxOH1PruVrDkCxEHx_w0Zt8LWZo-1788932521.424066-1.0.1.1-issKyw0Ya7u1k49OmqNkpVCdMIPVRYXLpcZTJR2E4RovN5F0zAfOld7RO.NN0k8jQVZniv2majLVOP8W.tz7V2DC9J.CPIN4nUkZgImyo668j2wiW31p9CMtJh4dzBN1
.erhassa.com/ 1970-01-22
02:31:32
Name: _ga_404GXE7LR3
Value: GS2.1.s1788932522$o1$g0$t1788932522$j60$l0$h0
.erhassa.com/ 1970-01-22
02:31:32
Name: _ga
Value: GA1.1.278507790.1788932523
.google.com/ 1970-01-21
21:19:03
Name: NID
Value: 534=YTrdxyKCtknMsSeQPvyZcBwnTPMXqQTit8HYGk47M5wzQ2aj6gOYjCHc5rdMfh8TV6GAfJo6UBiu3jsoAe1xZY0hExPZDE-85QtdjzpTCsM07JLqBdeh6Cm6_eSXbxToc36JIK4ndObVV5wYTiS0FFzlfwLZ4ZQ5_pk4jy0K0UKuFZyRCGn6vnb00uBtZC13Ulx83Erjdxijj3w

3 Console Messages

A page may trigger messages to the console to be logged. These are often error messages about being unable to load a resource or execute a piece of JavaScript. Sometimes they also provide insight into the technology behind a website.

Source Level URL
Text
network error URL: https://assets.teepublic.com/assets/teepublicons/x_close_orange400-c1926221e50e7f6686d23ac344405449054e43f23d0f3306f15d8dfd546f999a.svg
Message:
Failed to load resource: the server responded with a status of 404 ()
security warning URL: https://apis.google.com/_/scs/abc-static/_/js/k=gapi.lb.en.8uXxGUoumbY.O/m=gapi_iframes,gapi_iframes_style_common/rt=j/sv=1/d=1/ed=1/rs=AHpOoo96qx3mL4tzGUOa-0q0udyPRqEAoA/cb=gapi.loaded_0?le=scs,fedcm_migration_mod(Line 172)
Message:
Failed to execute 'postMessage' on 'DOMWindow': The target origin provided ('https://www.teepublic.com') does not match the recipient window's origin ('https://erhassa.com').

Security Headers

This page lists any security headers set by the main page. If you want to understand what these mean and how to use them, head on over to this page

Header Value
Strict-Transport-Security max-age=31536000

Indicators

This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.

ahddong.org
apis.google.com
assets.teepublic.com
erhassa.com
gambar.caramel.in.net
www.google-analytics.com
www.google.com
www.googletagmanager.com
www.gstatic.com
142.251.156.119
159.89.206.1
167.99.66.65
2404:6800:4003:c01::65
2404:6800:4003:c11::61
2404:6800:4003:c11::8b
2a06:98c1:3103::6812:26a1
1259f54ed212e285e2788dc50877bf890e5e515628157c35d04bcd013b94d29d
1b364e96bbea76d041688d12226ed12a83de069f78ed930f224b94f87da35dcb
1d0c861ff2eeeac69e7cb798e5b03d59dcd95dd61b76d2daf316c08e3287d9d6
212c5ea5f38ddc6fdb73d6f759c919c20d7a310ed263443a476a5ac9ce3c6ff5
22494eb4f5fc2ef8c229b9df2e171990687e4837282655145cca0fa302af1278
27d579a00be0c030f7b1abc77d60b8bc28332af49f86f047db384e0fb7d75b08
2fced7f256590dcdf737de4d59e6ec64403decb57fe8a10f46823e330bd847e7
2ff36965d5c0e93e09e6b3549e587a907f7ee7a3037a5ca783e29ccdd13acd82
30ac72b3a0780512f20d9702968b2ae6182c055f63b2bd87606deef0a8c170ed
3a851df453e952ce514b319769f4f2ad22e8a29ecb9e79d0dc4744f67f2b64fd
3e5e01f850c7dc8042ad991990dfef7059ad69f624a1c2660ce9f9b51bd585e5
3e63525c214d7d68ce1f129565ffe17758b4a608059eead6bbfa65900c7a4411
42ae886e435b0859e06afe4c42a690eb6e988dcc5d689a4c82546f0ed6274e94
4e6299640ff8b534bc90fc19548ca8caa977281c81797daa816a71127b633ccf
50949ab80f64ce02a76695926bfa9fc49a10edc926f927908b534d8efd42db6c
5ba0c95dc25e92dbd022b6fafd63bcc555056e24ec19d4c0a7a51cf61f52ff24
5ef586c8d4926e5c28868fb586be9160e68906b7385a8a7bc7ec04506a66fedf
62c1c0b235e26952857139537b65f8272026cd1c385c1bf6dba20481ee8a6619
63d5c76fcaa2c2a630aec6fac234d7a7b659605280e89cb98b92ee088fb5765d
6e2b26a8cd7d2009b9fcf9a29d1d700763d4c8137ce364e63d27527b8f50c2e7
717d0b286d5a89759167019ca1b0795dfc8c3801191d5d9f918aa9d12605324a
7364e8d42eb65f4df96e9b6a25dfe8832b1d7ccc8bf7983f958cff809b912ebb
778709e9f6ce30c8159d616dcaf4e4a1a586bae98323efe7980fe08a1a8e98bb
7893f701fbf393784062d3239223e80c7f989c9d7f993092f2527f0bc6d4f267
7ead77cf730b14f39e36d34bd0211644ce6e09fa8d90078b2b91a3eddd668c3b
80eac9665108a18e66b7754ffcae1c97eaa8b5516d680b596d290c8fd33260f4
899c1986f49fb1ff2436782e5f792471c5b7b290f43141e044c36cd7c9651696
8b386600aa0eb4c6398ee6f7f0f4040b53ec936b8aee73f27d0154a1ceb0379a
96598db6007ffda68026efb1c68800049c538747a82d87e8ee394c36ee40ee62
9684a25158374abc18c783c542321b64004bbd276157c159792dd929ebb87d5b
97ac201ffb076c59e7fd1e7ba2417e21b22d5bdfc4796265069f57cef05ce542
a8703732fc112fb61adbc3715a19ebc0944a5544c64ee314ade6140ec57ec644
ab8debe19f138dd26978779dceefc172902368b4cb943bc09d14fa6c01a6e322
b092b04d0f2c93375d3de1e2fe111af6706567d6abc1d7cfd8b57ad169a441cb
cd74472112978d7bafee49927769110f6f619373105d7f408add04b4098861cd
dbb92e32cb1a4c797c36c457f42e9a9b95998f659c02cec2a3f524a7ba34b0d6
dc107e99a4239bb6051cfc228578a1b2355cba1ea9b6fff08bec097159bed0c3
fca5865f91816cc63055735f94fe21c137902804167f8f0e49230d87a04ac7dc
fd4188121a6c9b28d029ebc07cd1db2f35e0657b4a2e825f901ed8b2b37bb327