
kpel965.com
2a02:26f0:7100::687e:2598
Public Scan
Open in
urlscan Pro
https://acadianafirstalert.com/ 4yr old
Effective URL:
https://kpel965.com/category/hurricane-season/ 9yr old
Submission: On September 09 via automatic, source certstream-suspicious (September 9th 2026, 8:35:14 am UTC) — Scanned from AT Go Pro
Only in urlscan Pro
- Select different country locations for Private Scans.
- Use a global network of additional scanning locations and residential IPs for scanning.
- Interact with pages while you are scanning them.
- Download files from remote websites.
- Scan websites on the Tor Network.
Summary
TLS certificate: Issued by YE2 on August 23rd 2026. Valid for: 3mo.
This is the only time kpel965.com was scanned on urlscan.io!
urlscan.io Verdict: No classification
Domain & IP information
| IP Address | AS Autonomous System | ||
|---|---|---|---|
| 1 1 | 216.152.143.250 216.152.143.250 | 13768 (COGECO-PEER1) (COGECO-PEER1 - Aptum Technologies) | |
| 35 | 2a02:26f0:710... 2a02:26f0:7100::687e:2598 | 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.) | |
| 13 | 2a02:26f0:fa0... 2a02:26f0:fa00::214:87a3 | 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.) | |
| 1 | 2a00:1450:400... 2a00:1450:4001:c21::5f | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 4 | 18.245.31.35 18.245.31.35 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 1 | 2a06:98c1:310... 2a06:98c1:310d::ac40:98f3 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 5 | 2a00:1450:400... 2a00:1450:4001:c0f::61 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 1 | 157.240.0.63 157.240.0.63 | 32934 (FACEBOOK) (FACEBOOK - Facebook) | |
| 1 | 157.240.0.174 157.240.0.174 | 32934 (FACEBOOK) (FACEBOOK - Facebook) | |
| 1 | 2606:4700:440... 2606:4700:4401::6812:291e | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 3 | 142.251.20.154 142.251.20.154 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 104.18.25.18 104.18.25.18 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 4 | 2a02:26f0:e30... 2a02:26f0:e300::215:2173 | 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.) | |
| 1 | 2600:9000:275... 2600:9000:275d:3200:0:bd73:4880:93a1 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 3 | 142.251.13.94 142.251.13.94 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 2a04:4e42:600... 2a04:4e42:600::720 | 54113 (FASTLY) (FASTLY - Fastly) | |
| 1 | 18.245.31.112 18.245.31.112 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 1 | 2600:1901:0:a... 2600:1901:0:ab09::1 | 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC) | |
| 11 | 2606:4700:10:... 2606:4700:10::6814:2f50 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 7 | 142.251.14.149 142.251.14.149 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 2 | 34.36.200.111 34.36.200.111 | 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC) | |
| 1 | 2606:4700:10:... 2606:4700:10::ac42:ab85 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 2a02:26f0:e30... 2a02:26f0:e300::215:2188 | 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.) | |
| 1 | 146.75.120.157 146.75.120.157 | 54113 (FASTLY) (FASTLY - Fastly) | |
| 2 | 142.251.127.155 142.251.127.155 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 2 | 2a02:26f0:2b8... 2a02:26f0:2b80:2f::215:8f4f | 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.) | |
| 1 | 162.159.140.229 162.159.140.229 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 65.9.130.110 65.9.130.110 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 2 | 3.174.46.116 3.174.46.116 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 1 2 | 2606:4700::68... 2606:4700::6812:116 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 108.138.4.226 108.138.4.226 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 1 | 3.248.137.33 3.248.137.33 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 2 | 34.110.146.185 34.110.146.185 | 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC) | |
| 2 | 98.91.154.91 98.91.154.91 | 14618 (AMAZON-AES) (AMAZON-AES - Amazon.com) | |
| 1 1 | 151.101.194.132 151.101.194.132 | 54113 (FASTLY) (FASTLY - Fastly) | |
| 1 | 23.207.210.138 23.207.210.138 | 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.) | |
| 10 | 54.170.116.67 54.170.116.67 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 5 | 2001:4860:480... 2001:4860:4802:34::36 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 151.101.192.84 151.101.192.84 | 54113 (FASTLY) (FASTLY - Fastly) | |
| 2 | 130.211.23.194 130.211.23.194 | 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC) | |
| 1 | 142.251.13.97 142.251.13.97 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 137 | 39 |
ASN13768 (COGECO-PEER1 - Aptum Technologies, CA)
| acadianafirstalert.com 4yr old |
ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL)
| kpel965.com 9yr old |
ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL)
| townsquare.media 8yr old |
ASN15169 (GOOGLE - Google LLC, US)
| fonts.googleapis.com 10yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-18-245-31-35.fra56.r.cloudfront.net
| cmp.osano.com 7yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| 40ba8f49-f119-4c3e-8d3a-08e85c30ef88.edge.permutive.app 8mo old |
ASN15169 (GOOGLE - Google LLC, US)
| www.googletagmanager.com 14yr old |
ASN32934 (FACEBOOK - Facebook, Inc., US)
PTR: instagram-p3-shv-02-fra3.fbcdn.net
| platform.instagram.com 12yr old |
ASN32934 (FACEBOOK - Facebook, Inc., US)
PTR: instagram-p42-shv-02-fra3.fbcdn.net
| www.instagram.com 10yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| cadmus.script.ac 4yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: bx-in-f154.1e100.net
| securepubads.g.doubleclick.net 10yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| js-sec.indexww.com 12yr old |
ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL)
| cdn.production.townsquareblogs.com 9yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
| www.nhc.noaa.gov 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: wt-in-f94.1e100.net
| fonts.gstatic.com 10yr old |
ASN54113 (FASTLY - Fastly, Inc., US)
| images.unsplash.com 11yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-18-245-31-112.fra56.r.cloudfront.net
| cmp.osano.com 7yr old |
ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US)
| driftingchef.com 4yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| ad-delivery.net 9yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: pm-in-f149.1e100.net
| ad.doubleclick.net 10yr old |
ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US)
PTR: 111.200.36.34.bc.googleusercontent.com
| ab.dns-finder.com 1yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| cdn.api.btloader.com 8mo old |
ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL)
| assets.pinterest.com 12yr old |
ASN54113 (FASTLY - Fastly, Inc., US)
| platform.twitter.com 14yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: lcfrai-in-f155.1e100.net
| pagead2.googlesyndication.com 10yr old |
ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL)
| 973thedawg.com 8yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| syndication.twitter.com 13yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-65-9-130-110.fra60.r.cloudfront.net
| assets.revcontent.com 7yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-3-174-46-116.fra60.r.cloudfront.net
| trends.revcontent.com 10yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| unpkg.com 10yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-108-138-4-226.fra56.r.cloudfront.net
| aax.amazon-adsystem.com 13yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: ec2-3-248-137-33.eu-west-1.compute.amazonaws.com
| trendsp.revcontent.com 2mo old |
ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US)
PTR: 185.146.110.34.bc.googleusercontent.com
| driftingchef.com 4yr old |
ASN14618 (AMAZON-AES - Amazon.com, Inc., US)
PTR: ec2-98-91-154-91.compute-1.amazonaws.com
| k.p-n.io 8yr old |
ASN54113 (FASTLY - Fastly, Inc., US)
| a.teads.tv 10yr old |
ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL)
PTR: a23-207-210-138.deploy.static.akamaitechnologies.com
| static.teads.tv 8yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: ec2-54-170-116-67.eu-west-1.compute.amazonaws.com
| yeet.revcontent.com 5yr old |
ASN15169 (GOOGLE - Google LLC, US)
| region1.google-analytics.com 5yr old |
ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US)
PTR: 194.23.211.130.bc.googleusercontent.com
| api.btloader.com 6yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: wt-in-f97.1e100.net
| www.googletagmanager.com 14yr old |
| Apex Domain Subdomains |
Transfer | |
|---|---|---|
| 35 |
kpel965.com
kpel965.com 9yr old |
384 KB |
| 14 |
revcontent.com
assets.revcontent.com — Cisco Umbrella Rank: 25739 7yr old trends.revcontent.com — Cisco Umbrella Rank: 5849 10yr old trendsp.revcontent.com — Cisco Umbrella Rank: 28217 2mo old yeet.revcontent.com — Cisco Umbrella Rank: 33834 5yr old |
5 KB |
| 13 |
townsquare.media
townsquare.media — Cisco Umbrella Rank: 115869 8yr old |
586 KB |
| 11 |
ad-delivery.net
ad-delivery.net — Cisco Umbrella Rank: 1937 9yr old |
2 KB |
| 10 |
doubleclick.net
securepubads.g.doubleclick.net — Cisco Umbrella Rank: 385 10yr old ad.doubleclick.net — Cisco Umbrella Rank: 180 10yr old |
272 KB |
| 6 |
googletagmanager.com
www.googletagmanager.com — Cisco Umbrella Rank: 64 14yr old |
938 KB |
| 5 |
google-analytics.com
region1.google-analytics.com — Cisco Umbrella Rank: 2487 5yr old |
|
| 5 |
osano.com
cmp.osano.com — Cisco Umbrella Rank: 5601 7yr old |
125 KB |
| 4 |
townsquareblogs.com
cdn.production.townsquareblogs.com — Cisco Umbrella Rank: 228659 9yr old |
140 KB |
| 3 |
btloader.com
cdn.api.btloader.com — Cisco Umbrella Rank: 2440 8mo old api.btloader.com — Cisco Umbrella Rank: 1996 6yr old |
448 B |
| 3 |
driftingchef.com
driftingchef.com 4yr old |
43 KB |
| 3 |
gstatic.com
fonts.gstatic.com — Cisco Umbrella Rank: 55 10yr old |
139 KB |
| 2 |
teads.tv
1 redirects
a.teads.tv — Cisco Umbrella Rank: 2004 10yr old static.teads.tv — Cisco Umbrella Rank: 4918 8yr old |
4 KB |
| 2 |
p-n.io
k.p-n.io — Cisco Umbrella Rank: 7886 8yr old |
|
| 2 |
unpkg.com
1 redirects
unpkg.com — Cisco Umbrella Rank: 902 10yr old |
3 KB |
| 2 |
973thedawg.com
973thedawg.com 8yr old |
8 KB |
| 2 |
googlesyndication.com
pagead2.googlesyndication.com — Cisco Umbrella Rank: 158 10yr old |
56 KB |
| 2 |
twitter.com
platform.twitter.com — Cisco Umbrella Rank: 2074 14yr old syndication.twitter.com — Cisco Umbrella Rank: 2581 13yr old |
104 KB |
| 2 |
pinterest.com
assets.pinterest.com — Cisco Umbrella Rank: 5474 12yr old log.pinterest.com — Cisco Umbrella Rank: 9575 10yr old |
19 KB |
| 2 |
dns-finder.com
ab.dns-finder.com — Cisco Umbrella Rank: 2241 1yr old |
214 B |
| 2 |
instagram.com
1 redirects
platform.instagram.com — Cisco Umbrella Rank: 17460 12yr old www.instagram.com — Cisco Umbrella Rank: 695 10yr old |
34 KB |
| 1 |
amazon-adsystem.com
aax.amazon-adsystem.com — Cisco Umbrella Rank: 2199 13yr old |
304 B |
| 1 |
unsplash.com
images.unsplash.com — Cisco Umbrella Rank: 12567 11yr old |
136 KB |
| 1 |
noaa.gov
www.nhc.noaa.gov — Cisco Umbrella Rank: 25053 10yr old |
141 KB |
| 1 |
indexww.com
js-sec.indexww.com — Cisco Umbrella Rank: 1287 12yr old |
11 KB |
| 1 |
script.ac
cadmus.script.ac — Cisco Umbrella Rank: 5100 4yr old |
226 B |
| 1 |
permutive.app
40ba8f49-f119-4c3e-8d3a-08e85c30ef88.edge.permutive.app — Cisco Umbrella Rank: 355139 8mo old |
163 KB |
| 1 |
googleapis.com
fonts.googleapis.com — Cisco Umbrella Rank: 67 10yr old |
3 KB |
| 1 |
acadianafirstalert.com
1 redirects
acadianafirstalert.com 4yr old |
285 B |
| 137 | 29 |
| Domain | Requested by | |
|---|---|---|
| 35 | kpel965.com |
kpel965.com
cmp.osano.com |
| 13 | townsquare.media |
kpel965.com
|
| 11 | ad-delivery.net |
kpel965.com
|
| 10 | yeet.revcontent.com |
kpel965.com
|
| 7 | ad.doubleclick.net |
kpel965.com
|
| 6 | www.googletagmanager.com |
kpel965.com
cmp.osano.com |
| 5 | region1.google-analytics.com |
kpel965.com
|
| 5 | cmp.osano.com |
kpel965.com
cmp.osano.com |
| 4 | cdn.production.townsquareblogs.com |
kpel965.com
cmp.osano.com cdn.production.townsquareblogs.com |
| 3 | driftingchef.com |
cmp.osano.com
driftingchef.com |
| 3 | fonts.gstatic.com |
fonts.googleapis.com
|
| 3 | securepubads.g.doubleclick.net |
kpel965.com
cmp.osano.com |
| 2 | api.btloader.com |
kpel965.com
|
| 2 | k.p-n.io |
kpel965.com
|
| 2 | unpkg.com |
1 redirects
kpel965.com
|
| 2 | trends.revcontent.com |
kpel965.com
|
| 2 | 973thedawg.com |
kpel965.com
|
| 2 | pagead2.googlesyndication.com |
kpel965.com
|
| 2 | ab.dns-finder.com |
kpel965.com
|
| 1 | log.pinterest.com |
kpel965.com
|
| 1 | static.teads.tv |
kpel965.com
|
| 1 | a.teads.tv | 1 redirects |
| 1 | trendsp.revcontent.com |
kpel965.com
|
| 1 | aax.amazon-adsystem.com |
driftingchef.com
|
| 1 | assets.revcontent.com |
cmp.osano.com
|
| 1 | syndication.twitter.com |
platform.twitter.com
|
| 1 | platform.twitter.com |
cmp.osano.com
|
| 1 | assets.pinterest.com |
cmp.osano.com
|
| 1 | cdn.api.btloader.com |
kpel965.com
|
| 1 | images.unsplash.com |
kpel965.com
|
| 1 | www.nhc.noaa.gov |
kpel965.com
|
| 1 | js-sec.indexww.com |
kpel965.com
|
| 1 | cadmus.script.ac |
kpel965.com
|
| 1 | www.instagram.com |
kpel965.com
|
| 1 | platform.instagram.com | 1 redirects |
| 1 | 40ba8f49-f119-4c3e-8d3a-08e85c30ef88.edge.permutive.app |
kpel965.com
|
| 1 | fonts.googleapis.com |
kpel965.com
|
| 1 | acadianafirstalert.com | 1 redirects |
| 137 | 38 |
This site contains links to these domains. Also see Links.
| Domain |
|---|
| townsquarelafayette.threadless.com |
| www.google.com |
| www.facebook.com |
| www.instagram.com |
| youtube.com |
| twitter.com |
| www.laseagrant.org |
| publicfiles.fcc.gov |
| www.youtube.com |
| www.townsquaremedia.com |
| Subject Issuer | Validity | Valid | |
|---|---|---|---|
| kpel965.com YE2 |
2026-08-23 - 2026-11-21 |
3mo | crt.sh |
| townsquare.media YE2 |
2026-08-31 - 2026-11-29 |
3mo | crt.sh |
| upload.video.google.com WE2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| *.osano.com Amazon RSA 2048 M01 |
2026-07-19 - 2027-02-01 |
7mo | crt.sh |
| permutive.app WE1 |
2026-09-05 - 2026-12-04 |
3mo | crt.sh |
| *.google-analytics.com WE2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| script.ac YE2 |
2026-07-30 - 2026-10-28 |
3mo | crt.sh |
| *.g.doubleclick.net WE2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| indexww.com WE1 |
2026-07-13 - 2026-10-11 |
3mo | crt.sh |
| cdn.production.townsquareblogs.com YE1 |
2026-08-23 - 2026-11-21 |
3mo | crt.sh |
| www.nhc.noaa.gov Amazon RSA 2048 M01 |
2025-11-21 - 2026-12-20 |
1yr | crt.sh |
| *.gstatic.com WE2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| images.unsplash.com GlobalSign Atlas R46 DV TLS CA 2026 Q3 |
2026-07-30 - 2027-02-14 |
7mo | crt.sh |
| driftingchef.com YE2 |
2026-07-04 - 2026-10-02 |
3mo | crt.sh |
| ad-delivery.net WE1 |
2026-08-22 - 2026-11-20 |
3mo | crt.sh |
| *.doubleclick.net WE2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| ab.dns-finder.com WR3 |
2026-07-18 - 2026-10-16 |
3mo | crt.sh |
| btloader.com WE1 |
2026-07-28 - 2026-10-26 |
3mo | crt.sh |
| *.pinimg.com DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2026-06-22 - 2027-01-06 |
7mo | crt.sh |
| *.twimg.com YR2 |
2026-08-01 - 2026-10-30 |
3mo | crt.sh |
| 973thedawg.com YE2 |
2026-08-22 - 2026-11-20 |
3mo | crt.sh |
| *.twitter.com YR1 |
2026-08-14 - 2026-11-12 |
3mo | crt.sh |
| revcontent.com Amazon RSA 2048 M04 |
2026-02-18 - 2027-03-19 |
1yr | crt.sh |
| alt1-3ps.amazon-adsystem.com Amazon RSA 2048 M01 |
2026-07-17 - 2027-01-30 |
7mo | crt.sh |
| trends.revcontent.dev YR2 |
2026-08-10 - 2026-11-08 |
3mo | crt.sh |
| k.p-n.io Amazon RSA 2048 M04 |
2025-11-17 - 2026-12-16 |
1yr | crt.sh |
| yeet.revcontent.com YR1 |
2026-08-05 - 2026-11-03 |
3mo | crt.sh |
| *.pinterest.com DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2026-08-13 - 2027-02-26 |
7mo | crt.sh |
| api.btloader.com WR3 |
2026-08-15 - 2026-11-13 |
3mo | crt.sh |
This page contains 4 frames:
Primary Page:
https://kpel965.com/category/hurricane-season/
Frame ID: C3445F8F95404F8924908D1371DCAA2D
Requests: 125 HTTP requests in this frame
Frame:
https://cdn.production.townsquareblogs.com/aleph/
Frame ID: DD1ED56F15CDA07D58C809824DC6C80B
Requests: 3 HTTP requests in this frame
Frame:
https://cmp.osano.com/
Frame ID: BF1E3EA6E51EFEE52BFF68651F77B3A3
Requests: 1 HTTP requests in this frame
Frame:
https://platform.twitter.com/widgets/widget_iframe.1227a5674072e080ffb1ba14ac0c1079.html?origin=https%3A%2F%2Fkpel965.com
Frame ID: 021515D375A4D7B40FB22CE947579BC3
Requests: 2 HTTP requests in this frame
Screenshot
Go Pro
Only in urlscan Pro
Use the Visual Search feature to find pages with visually similar screenshots.
Click for more information
Free trials of urlscan Pro are available.
Page Title
Hurricane Season - KPEL 96.5Page URL History
Go Pro
Only in urlscan Pro
Search our real-time database of newly observed domains and
hostnames. Pivot on different attributes, and setup keyword alerts for
newly observed domains.
Click for more information
Free trials of urlscan Pro are available.
Show full URLs
-
https://acadianafirstalert.com/
HTTP 302
https://kpel965.com/category/hurricane-season/ Page URL
Detected technologies
 WordPress
(CMS)
Expand
Detected patterns
- /wp-(?:content|includes)/
 Amazon Advertising
(Advertising)
Expand
Detected patterns
- \.amazon-adsystem\.com
 Cloudflare Bot Management
(Security)
Expand
Detected patterns
 DoubleClick Floodlight
(Advertising)
Expand
Detected patterns
- \.doubleclick\.net
 Google AdSense
(Advertising)
Expand
Detected patterns
- googlesyndication\.com/
 Google Analytics
(Analytics)
Expand
Detected patterns
- googletagmanager\.com/gtag/js
 Google Publisher Tag
(Advertising)
Expand
Detected patterns
- securepubads\.g\.doubleclick.net/tag/js/gpt\.js
 Google Tag Manager
(Tag managers)
Expand
Detected patterns
- googletagmanager\.com/gtm\.js
- \.googletagmanager\.com/
 Osano
(Cookie compliance)
Expand
Detected patterns
- cmp\.osano\.com/
 Teads
(Advertising)
Expand
Detected patterns
- teads\.tv
 Unpkg
(CDN)
Expand
Detected patterns
- unpkg\.com/
 web-vitals
(JavaScript libraries)
Expand
Detected patterns
- web-vitals@([\d.]+)/dist/web-vitals.*\.js
Page Statistics
10 Outgoing links
Go Pro
Only in urlscan Pro
Effortlessly use any on-page link as a pivot to discover other pages pointing to the exact same destination. Seamlessly trace both specific URLs and broader domains to uncover hidden connection networks and map out backlink relationships with ease.
Click for more information
Free trials of urlscan Pro are available.
These are links going to different origins than the main page.
Title: KPEL Merch
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Title: Hurricane Resource guide
Search URL Search Domain Scan URL
Title: Public File
Search URL Search Domain Scan URL
Title: Visit us on Youtube
Search URL Search Domain Scan URL
Title: , Townsquare Media, Inc
Search URL Search Domain Scan URL
Page URL History
This captures the URL locations of the websites, including HTTP redirects and client-side redirects via JavaScript or Meta fields.
-
https://acadianafirstalert.com/
HTTP 302
https://kpel965.com/category/hurricane-season/ Page URL
Redirected requests
There were HTTP redirect chains for the following requests:
Request Chain 9- https://platform.instagram.com/en_US/embeds.js HTTP 301
- https://www.instagram.com/embed.js
- https://unpkg.com/web-vitals@4?/dist/web-vitals.umd.js HTTP 302
- https://unpkg.com/web-vitals@4.2.4/dist/web-vitals.iife.js?%2Fdist%2Fweb-vitals.umd.js=
- https://a.teads.tv/analytics/tag.js HTTP 301
- https://static.teads.tv/analytics/tag.js
137 HTTP transactions
Go Pro
Only in urlscan Pro
Inspect WebSocket connections, examine POST data effortlessly, and track overlap counts in real time. Features live search and filtering across all HTTP output, complete with full response metadata for deep analysis.
Click for more information
Free trials of urlscan Pro are available.
0 data transactions
| Method Protocol |
Status | Resource Path |
Size x-fer |
Time Latency |
Type MIME-Type |
IP Location |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
|
GET H2 |
200 |
Primary Request
/
Show response
kpel965.com/category/hurricane-season/ Redirect Chain
|
250 KB 50 KB |
187ms
46ms |
Document
text/html |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
base.css
kpel965.com/styles/desktop/ |
304 KB 44 KB |
62ms
60ms |
Stylesheet
text/css |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
main.bundle.1bda4cfdc494d1fcb247fdf549ebca07.js
Show response
townsquare.media/public/dist/desktop/ |
658 KB 181 KB |
410ms
158ms |
Script
application/javascript |
2a02:26f0:fa00::214:87a3 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
css
fonts.googleapis.com/ |
46 KB 3 KB |
146ms
47ms |
Stylesheet
text/css |
2a00:1450:4001:c21::5f Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
osano.js
Show response
cmp.osano.com/AzZv96TckxjKF6VSR/b22a3c1e-9330-420c-a146-9d99b80cfddc/ |
365 KB 80 KB |
118ms
35ms |
Script
application/javascript |
18.245.31.35 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
40ba8f49-f119-4c3e-8d3a-08e85c30ef88-web.js
Show response
40ba8f49-f119-4c3e-8d3a-08e85c30ef88.edge.permutive.app/ |
716 KB 163 KB |
102ms
33ms |
Script
application/javascript |
2a06:98c1:310d::ac40:98f3 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
gtm.js
Show response
www.googletagmanager.com/ |
480 KB 146 KB |
140ms
66ms |
Script
application/javascript |
2a00:1450:4001:c0f::61 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
larimda.js
Show response
kpel965.com/ |
5 KB 2 KB |
34ms
32ms |
Script
text/javascript |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
scripts.js
Show response
kpel965.com/rest/carbon/api/ |
549 KB 154 KB |
56ms
54ms |
Script
text/javascript |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
scripts.js
Show response
kpel965.com/rest/carbon/api/ |
171 KB 51 KB |
35ms
33ms |
Script
text/javascript |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
embed.js
Show response
www.instagram.com/ Redirect Chain
|
104 KB 34 KB |
243ms
193ms |
Script
application/x-javascript |
157.240.0.174 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
script.js
Show response
cadmus.script.ac/d20yokc2jf6ta9/ |
3 B 226 B |
85ms
28ms |
Script
application/javascript |
2606:4700:4401::6812:291e Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
gpt.js
Show response
securepubads.g.doubleclick.net/tag/js/ |
120 KB 37 KB |
103ms
52ms |
Script
text/javascript |
142.251.20.154 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
186854-113710634486999.js
Show response
js-sec.indexww.com/ht/p/ |
32 KB 11 KB |
83ms
32ms |
Script
application/javascript |
104.18.25.18 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
pb.js
Show response
cdn.production.townsquareblogs.com/wp-content/uploads/static/prebid/carbon/ |
448 KB 138 KB |
239ms
81ms |
Script
application/javascript |
2a02:26f0:e300::215:2173 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
kpel.png
townsquare.media/site/36/files/2018/08/ |
33 KB 33 KB |
322ms
71ms |
Image
image/webp |
2a02:26f0:fa00::214:87a3 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
two_atl_0d0.png
www.nhc.noaa.gov/xgtwo/ |
140 KB 141 KB |
584ms
470ms |
Image
image/png |
2600:9000:275d:3200:0:bd73:4880:93a1 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
cogitoergosum
Show response
kpel965.com/rest/high/api/ |
128 B 640 B |
414ms
413ms |
XHR
application/json |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
ae238523-ed14-4a06-8669-39a94d68d5c1
https://kpel965.com/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
/
Show response
cdn.production.townsquareblogs.com/aleph/ Frame DD1E |
3 KB 985 B |
264ms
169ms |
Document
text/html |
2a02:26f0:e300::215:2173 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
kpel965_background.jpg
townsquare.media/site/36/files/2017/09/ |
56 KB 56 KB |
190ms
189ms |
Image
image/webp |
2a02:26f0:fa00::214:87a3 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
kpel.png
townsquare.media/site/36/files/2018/08/ |
33 KB 0 |
1ms
1ms |
Image
image/webp |
2a02:26f0:fa00::214:87a3 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
KFO7CnqEu92Fr1ME7kSn66aGLdTylUAMa3yUBA.woff2
fonts.gstatic.com/s/roboto/v51/ |
42 KB 42 KB |
89ms
35ms |
Font
font/woff2 |
142.251.13.94 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
ieVl2ZhZI2eCN5jzbjEETS9weq8-19K7DQ.woff2
fonts.gstatic.com/s/robotocondensed/v31/ |
50 KB 50 KB |
98ms
45ms |
Font
font/woff2 |
142.251.13.94 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
attachment-09-sep-satt-gulf.JPG
townsquare.media/site/33/files/2026/09/ |
70 KB 71 KB |
219ms
217ms |
Image
image/webp |
2a02:26f0:fa00::214:87a3 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Storm-Clouds-5-a.jpg
townsquare.media/site/33/files/2020/06/ |
16 KB 17 KB |
207ms
205ms |
Image
image/webp |
2a02:26f0:fa00::214:87a3 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
photo-1689222485261-4120a5974ff0
images.unsplash.com/ |
136 KB 136 KB |
78ms
22ms |
Image
image/jpeg |
2a04:4e42:600::720 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
attachment-gettyimages-2282066656-2.jpg
townsquare.media/site/33/files/2026/08/ |
46 KB 46 KB |
218ms
216ms |
Image
image/webp |
2a02:26f0:fa00::214:87a3 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
attachment-gettyimages-183110561.jpg
townsquare.media/site/33/files/2026/08/ |
85 KB 86 KB |
180ms
179ms |
Image
image/webp |
2a02:26f0:fa00::214:87a3 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
attachment-bertha-sat-pic.JPG
townsquare.media/site/33/files/2026/07/ |
59 KB 59 KB |
211ms
209ms |
Image
image/webp |
2a02:26f0:fa00::214:87a3 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
/
Show response
cmp.osano.com/ Frame BF1E |
5 KB 1 KB |
66ms
33ms |
Document
text/html |
18.245.31.112 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
osano-ui.js
Show response
cmp.osano.com/AzZv96TckxjKF6VSR/b22a3c1e-9330-420c-a146-9d99b80cfddc/ |
131 KB 33 KB |
35ms
34ms |
Script
application/javascript |
18.245.31.35 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
de-at.json
Show response
cmp.osano.com/AzZv96TckxjKF6VSR/b22a3c1e-9330-420c-a146-9d99b80cfddc/ |
36 KB 11 KB |
37ms
37ms |
XHR
application/json |
18.245.31.35 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
OPTIONS H3 |
200 |
de-at.json
cmp.osano.com/AzZv96TckxjKF6VSR/b22a3c1e-9330-420c-a146-9d99b80cfddc/ Frame |
0 0 |
340ms
306ms |
Preflight
|
18.245.31.35 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
gdbhnyncci3f.main.js
Show response
driftingchef.com/public/ |
123 KB 43 KB |
171ms
59ms |
Script
text/javascript |
2600:1901:0:ab09::1 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
px.gif
Show response
ad-delivery.net/ |
43 B 109 B |
87ms
29ms |
Fetch
image/gif |
2606:4700:10::6814:2f50 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
favicon.ico
Show response
ad.doubleclick.net/ |
1 KB 129 B |
85ms
43ms |
Fetch
image/x-icon |
142.251.14.149 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
px.gif
Show response
ad-delivery.net/ |
43 B 616 B |
83ms
27ms |
Fetch
image/gif |
2606:4700:10::6814:2f50 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
dns
Show response
ab.dns-finder.com/meta/ |
2 B 214 B |
245ms
152ms |
Fetch
text/plain |
34.36.200.111 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
device
Show response
cdn.api.btloader.com/ |
87 B 295 B |
142ms
84ms |
Fetch
application/json |
2606:4700:10::ac42:ab85 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
77317754-5d87-4219-8369-63501210b1d3
https://kpel965.com/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
pinit_main.js
Show response
assets.pinterest.com/js/ |
66 KB 19 KB |
123ms
28ms |
Script
application/javascript |
2a02:26f0:e300::215:2188 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
widget_iframe.1227a5674072e080ffb1ba14ac0c1079.html
Show response
platform.twitter.com/widgets/ Frame 0215 |
319 KB 103 KB |
132ms
31ms |
Document
text/html |
146.75.120.157 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
pubads_impl.js
Show response
securepubads.g.doubleclick.net/pagead/managed/js/gpt/m202609040101/ |
689 KB 212 KB |
34ms
33ms |
Script
text/javascript |
142.251.20.154 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
cogitoergosum
Show response
kpel965.com/rest/high/api/ |
128 B 519 B |
153ms
151ms |
Fetch
application/json |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
chunk-81.ff0e2e8ff13778c015fe.1788472146625.js
Show response
kpel965.com/public/dist/chunks/ |
470 B 679 B |
38ms
38ms |
Script
application/javascript |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
chunk-19.6c446ad4fdf85e7c67b7.1788472146625.js
Show response
kpel965.com/public/dist/chunks/ |
4 KB 2 KB |
38ms
37ms |
Script
application/javascript |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
chunk-82.82626c1980014cb5d6f4.1788472146625.js
Show response
kpel965.com/public/dist/chunks/ |
1 KB 872 B |
40ms
39ms |
Script
application/javascript |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
chunk-35.e2dcdf94d744430f1897.1788472146625.js
Show response
kpel965.com/public/dist/chunks/ |
799 B 805 B |
42ms
42ms |
Script
application/javascript |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
chunk-40.f5c1071fbfa025b82d2d.1788472146625.js
Show response
kpel965.com/public/dist/chunks/ |
963 B 840 B |
38ms
38ms |
Script
application/javascript |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
chunk-41.ed52506e5dcbfd730993.1788472146625.js
Show response
kpel965.com/public/dist/chunks/ |
605 B 744 B |
46ms
46ms |
Script
application/javascript |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
chunk-36.e019df1464f7a4d89b66.1788472146625.js
Show response
kpel965.com/public/dist/chunks/ |
630 B 776 B |
46ms
44ms |
Script
application/javascript |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
chunk-53.c6d8b39b02ebf02cbff0.1788472146625.js
Show response
kpel965.com/public/dist/chunks/ |
40 KB 12 KB |
36ms
34ms |
Script
application/javascript |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
chunk-44.c3b1c5578d8a50c64d90.1788472146625.js
Show response
kpel965.com/public/dist/chunks/ |
26 KB 8 KB |
38ms
37ms |
Script
application/javascript |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
chunk-83.b106955a99a199f9557f.1788472146625.js
Show response
kpel965.com/public/dist/chunks/ |
900 B 834 B |
63ms
62ms |
Script
application/javascript |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
chunk-77.68f96506782012d187ee.1788472146625.js
Show response
kpel965.com/public/dist/chunks/ |
1 KB 989 B |
36ms
36ms |
Script
application/javascript |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
chunk-37.be0e44c06c4d4619b262.1788472146625.js
Show response
kpel965.com/public/dist/chunks/ |
65 KB 16 KB |
56ms
56ms |
Script
application/javascript |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
chunk-31.e82b83c7902a426942c6.1788472146625.js
Show response
kpel965.com/public/dist/chunks/ |
7 KB 3 KB |
52ms
52ms |
Script
application/javascript |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
chunk-26.418942a7906d2d322c8f.1788472146625.js
Show response
kpel965.com/public/dist/chunks/ |
70 KB 16 KB |
60ms
60ms |
Script
application/javascript |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
chunk-86.8f6899e772bfa4cefe37.1788472146625.js
Show response
kpel965.com/public/dist/chunks/ |
926 B 823 B |
50ms
49ms |
Script
application/javascript |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
chunk-87.37434c92534accbee06b.1788472146625.js
Show response
kpel965.com/public/dist/chunks/ |
3 KB 2 KB |
75ms
75ms |
Script
application/javascript |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
adsbygoogle.js
Show response
pagead2.googlesyndication.com/pagead/js/ |
162 KB 56 KB |
97ms
54ms |
Fetch
text/javascript |
142.251.127.155 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
/
Show response
kpel965.com/internal-ad-api/ |
2 KB 736 B |
589ms
589ms |
Fetch
application/json |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
Untitled-design-5.jpg
townsquare.media/site/36/files/2020/08/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Dawg-Bruce-copy1.jpg
973thedawg.com/files/2017/06/ |
7 KB 8 KB |
575ms
420ms |
Image
image/webp |
2a02:26f0:2b80:2f::215:8f4f AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Dawg-Bruce-copy1.jpg
townsquare.media/site/33/files/2017/06/ |
17 KB 18 KB |
68ms
67ms |
Image
image/webp |
2a02:26f0:fa00::214:87a3 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
cogitoergosum
Show response
cdn.production.townsquareblogs.com/rest/high/api/ Frame DD1E |
281 B 748 B |
158ms
156ms |
Fetch
application/json |
2a02:26f0:e300::215:2173 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
cogitoergosum
Show response
cdn.production.townsquareblogs.com/rest/high/api/ Frame DD1E |
281 B 753 B |
353ms
352ms |
Fetch
application/json |
2a02:26f0:e300::215:2173 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
settings
Show response
syndication.twitter.com/ Frame 0215 |
869 B 963 B |
213ms
146ms |
Fetch
application/json |
162.159.140.229 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
chunk-97.19c0fd33c8e056152cdf.1788472146625.js
Show response
kpel965.com/public/dist/chunks/ |
596 B 747 B |
36ms
35ms |
Script
application/javascript |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
chunk-85.638f1fa877f769b72e60.1788472146625.js
Show response
kpel965.com/public/dist/chunks/ |
766 B 770 B |
40ms
39ms |
Script
application/javascript |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
chunk-48.c5dcc736fe73a89b502f.1788472146625.js
Show response
kpel965.com/public/dist/chunks/ |
720 B 795 B |
33ms
33ms |
Script
application/javascript |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
chunk-49.e30cc280178772a4e422.1788472146625.js
Show response
kpel965.com/public/dist/chunks/ |
711 B 795 B |
34ms
34ms |
Script
application/javascript |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
chunk-75.255cbe9fc48f94a1a665.1788472146625.js
Show response
kpel965.com/public/dist/chunks/ |
3 KB 1 KB |
34ms
34ms |
Script
application/javascript |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
kpel965_promo.jpg
townsquare.media/site/36/files/2017/09/ |
3 KB 3 KB |
67ms
67ms |
Image
image/webp |
2a02:26f0:fa00::214:87a3 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
px.gif
Show response
ad-delivery.net/ |
43 B 110 B |
30ms
30ms |
Fetch
image/gif |
2606:4700:10::6814:2f50 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
attachment-louisiana-campgrounds.jpg
townsquare.media/site/36/files/2024/04/ |
13 KB 13 KB |
69ms
69ms |
Image
image/webp |
2a02:26f0:fa00::214:87a3 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
cogitoergosum
Show response
kpel965.com/rest/high/api/ |
22 B 270 B |
220ms
219ms |
Fetch
application/json |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
px.png
assets.revcontent.com/master/assets/ |
95 B 489 B |
108ms
33ms |
Image
image/png |
65.9.130.110 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
/
Show response
trends.revcontent.com/api/demand/ |
73 B 488 B |
151ms
58ms |
Fetch
application/json |
3.174.46.116 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
js
Show response
www.googletagmanager.com/gtag/ |
444 KB 154 KB |
62ms
60ms |
Script
application/javascript |
2a00:1450:4001:c0f::61 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
js
Show response
www.googletagmanager.com/gtag/ |
477 KB 162 KB |
78ms
77ms |
Script
application/javascript |
2a00:1450:4001:c0f::61 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
js
Show response
www.googletagmanager.com/gtag/ |
462 KB 157 KB |
84ms
84ms |
Script
application/javascript |
2a00:1450:4001:c0f::61 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
js
Show response
www.googletagmanager.com/gtag/ |
476 KB 162 KB |
91ms
91ms |
Script
application/javascript |
2a00:1450:4001:c0f::61 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
web-vitals.iife.js
Show response
unpkg.com/web-vitals@4.2.4/dist/ Redirect Chain
|
7 KB 3 KB |
32ms
31ms |
Script
text/javascript |
2606:4700::6812:116 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
prebid
Show response
aax.amazon-adsystem.com/e/dtb/bid/681653.84/0/ |
19 B 304 B |
216ms
97ms |
Fetch
text/javascript |
108.138.4.226 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
gpt
securepubads.g.doubleclick.net/pagead/managed/dict/m202609080101/ |
64 KB 22 KB |
46ms
45ms |
Other
text/plain |
142.251.20.154 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
favicon.ico
Show response
ad.doubleclick.net/ |
1 KB 129 B |
48ms
47ms |
Fetch
image/x-icon |
142.251.14.149 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
px.gif
Show response
ad-delivery.net/ |
43 B 140 B |
27ms
27ms |
Fetch
image/gif |
2606:4700:10::6814:2f50 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
/
Show response
trends.revcontent.com/api/delivery/ |
7 KB 4 KB |
60ms
57ms |
Fetch
application/json |
3.174.46.116 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
impression
trendsp.revcontent.com/event/ |
0 0 |
170ms
54ms |
Fetch
|
3.248.137.33 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
200 |
paz3zjbd0r3y0h9skad2f5ks
Show response
driftingchef.com/ |
303 B 328 B |
110ms
58ms |
Fetch
application/json |
34.110.146.185 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
event-stream
k.p-n.io/ |
0 0 |
385ms
123ms |
Fetch
|
98.91.154.91 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
tag.js
Show response
static.teads.tv/analytics/ Redirect Chain
|
11 KB 4 KB |
151ms
32ms |
Script
text/javascript |
23.207.210.138 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Dawg-Bruce-copy1.jpg
973thedawg.com/files/2017/06/ |
7 KB 0 |
0ms
0ms |
Image
image/webp |
2a02:26f0:2b80:2f::215:8f4f AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
200 |
paz3zjbd0r3y0h9skad2f5ks
Show response
driftingchef.com/ |
16 B 40 B |
54ms
53ms |
Fetch
application/json |
34.110.146.185 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
event-stream
k.p-n.io/ |
0 0 |
124ms
123ms |
Fetch
|
98.91.154.91 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
OPTIONS H2 |
200 |
page-view
yeet.revcontent.com/yeet/events/ Frame |
0 0 |
165ms
53ms |
Preflight
|
54.170.116.67 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
OPTIONS H2 |
200 |
widget-loaded
yeet.revcontent.com/yeet/events/ Frame |
0 0 |
165ms
54ms |
Preflight
|
54.170.116.67 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
page-view
yeet.revcontent.com/yeet/events/ |
0 0 |
56ms
55ms |
Fetch
|
54.170.116.67 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
widget-loaded
yeet.revcontent.com/yeet/events/ |
0 0 |
54ms
53ms |
Fetch
|
54.170.116.67 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
px.gif
Show response
ad-delivery.net/ |
43 B 110 B |
28ms
28ms |
Fetch
image/gif |
2606:4700:10::6814:2f50 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
favicon.ico
Show response
ad.doubleclick.net/ |
1 KB 129 B |
45ms
45ms |
Fetch
image/x-icon |
142.251.14.149 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
px.gif
Show response
ad-delivery.net/ |
43 B 110 B |
29ms
29ms |
Fetch
image/gif |
2606:4700:10::6814:2f50 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
dns
Show response
ab.dns-finder.com/meta/ |
2 B 0 |
0ms
0ms |
Fetch
text/plain |
34.36.200.111 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
collect
region1.google-analytics.com/g/ |
0 0 |
109ms
41ms |
Fetch
text/plain |
2001:4860:4802:34::36 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
collect
region1.google-analytics.com/g/ |
0 0 |
107ms
43ms |
Fetch
text/plain |
2001:4860:4802:34::36 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
collect
region1.google-analytics.com/g/ |
0 0 |
100ms
43ms |
Fetch
text/plain |
2001:4860:4802:34::36 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
collect
region1.google-analytics.com/g/ |
0 0 |
95ms
44ms |
Fetch
text/plain |
2001:4860:4802:34::36 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
204 |
ping
pagead2.googlesyndication.com/pagead/ |
0 0 |
78ms
77ms |
Fetch
image/gif |
142.251.127.155 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
px.gif
Show response
ad-delivery.net/ |
43 B 133 B |
27ms
27ms |
Fetch
image/gif |
2606:4700:10::6814:2f50 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
/
log.pinterest.com/ |
0 388 B |
111ms
62ms |
Image
text/plain |
151.101.192.84 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
px.gif
Show response
ad-delivery.net/ |
43 B 116 B |
31ms
30ms |
Fetch
image/gif |
2606:4700:10::6814:2f50 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
favicon.ico
Show response
ad.doubleclick.net/ |
1 KB 129 B |
41ms
41ms |
Fetch
image/x-icon |
142.251.14.149 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
px.gif
Show response
ad-delivery.net/ |
43 B 111 B |
28ms
28ms |
Fetch
image/gif |
2606:4700:10::6814:2f50 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
favicon.ico
Show response
ad.doubleclick.net/ |
1 KB 129 B |
43ms
43ms |
Fetch
image/x-icon |
142.251.14.149 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
vcpm-event
yeet.revcontent.com/yeet/events/ |
0 0 |
56ms
54ms |
Fetch
|
54.170.116.67 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
OPTIONS H2 |
200 |
vcpm-event
yeet.revcontent.com/yeet/events/ Frame |
0 0 |
54ms
54ms |
Preflight
|
54.170.116.67 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
vcpm-event
yeet.revcontent.com/yeet/events/ |
0 0 |
55ms
52ms |
Fetch
|
54.170.116.67 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
OPTIONS H2 |
200 |
vcpm-event
yeet.revcontent.com/yeet/events/ Frame |
0 0 |
53ms
53ms |
Preflight
|
54.170.116.67 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
vcpm-event
yeet.revcontent.com/yeet/events/ |
0 0 |
55ms
54ms |
Fetch
|
54.170.116.67 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
OPTIONS H2 |
200 |
vcpm-event
yeet.revcontent.com/yeet/events/ Frame |
0 0 |
53ms
53ms |
Preflight
|
54.170.116.67 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
px.gif
Show response
ad-delivery.net/ |
43 B 140 B |
28ms
27ms |
Fetch
image/gif |
2606:4700:10::6814:2f50 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
favicon.ico
Show response
ad.doubleclick.net/ |
1 KB 129 B |
44ms
43ms |
Fetch
image/x-icon |
142.251.14.149 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
px.gif
Show response
ad-delivery.net/ |
43 B 110 B |
32ms
32ms |
Fetch
image/gif |
2606:4700:10::6814:2f50 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
favicon.ico
Show response
ad.doubleclick.net/ |
1 KB 129 B |
41ms
41ms |
Fetch
image/x-icon |
142.251.14.149 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
country
Show response
api.btloader.com/ |
37 B 153 B |
225ms
152ms |
Fetch
application/json |
130.211.23.194 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
pv
api.btloader.com/ |
0 0 |
222ms
150ms |
Fetch
|
130.211.23.194 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
chunk-27.80c867f327ce46ddf9c8.1788472146625.js
Show response
kpel965.com/public/dist/chunks/ |
3 KB 1 KB |
35ms
35ms |
Script
application/javascript |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
chunk-32.6ace7d203ce3f34c0ca9.1788472146625.js
Show response
kpel965.com/public/dist/chunks/ |
29 KB 7 KB |
35ms
35ms |
Script
application/javascript |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
chunk-21.8ec07634e87443c712e2.1788472146625.js
Show response
kpel965.com/public/dist/chunks/ |
530 B 675 B |
40ms
40ms |
Script
application/javascript |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
cogitoergosum
Show response
kpel965.com/rest/high/api/ |
22 B 270 B |
155ms
155ms |
Fetch
application/json |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
chunk-59.e2aa8401982834cdfbda.1788472146625.js
Show response
kpel965.com/public/dist/chunks/ |
1 KB 952 B |
33ms
32ms |
Script
application/javascript |
2a02:26f0:7100::687e:2598 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
kpelfmlogov4mobile.png
townsquare.media/site/36/files/2015/07/ |
3 KB 4 KB |
68ms
68ms |
Image
image/webp |
2a02:26f0:fa00::214:87a3 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
KFO5CnqEu92Fr1Mu53ZEC9_Vu3r1gIhOszmkBnka.woff2
fonts.gstatic.com/s/roboto/v51/ |
46 KB 46 KB |
33ms
33ms |
Font
font/woff2 |
142.251.13.94 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
js
Show response
www.googletagmanager.com/gtag/ |
456 KB 157 KB |
66ms
66ms |
Script
application/javascript |
142.251.13.97 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
collect
region1.google-analytics.com/g/ |
0 0 |
42ms
41ms |
Fetch
text/plain |
2001:4860:4802:34::36 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||




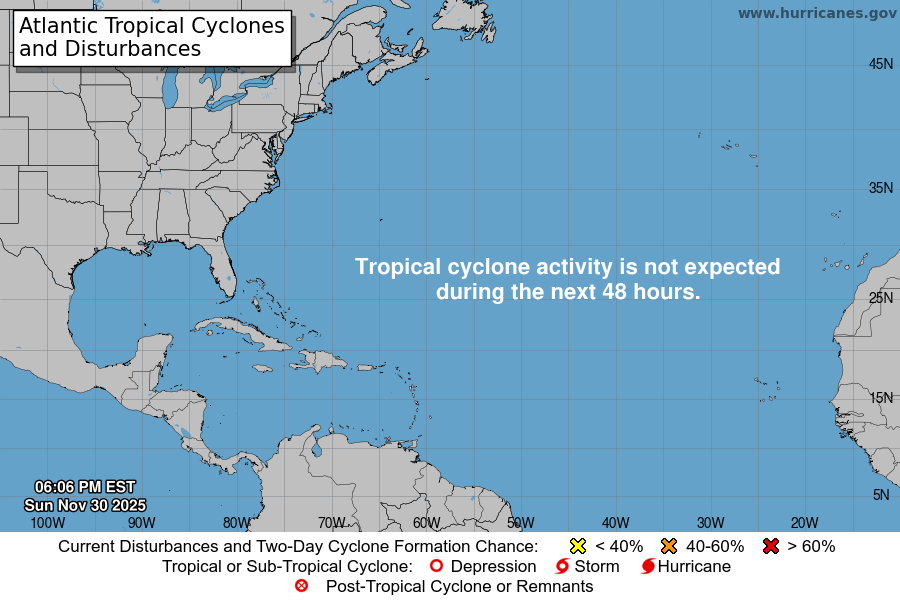






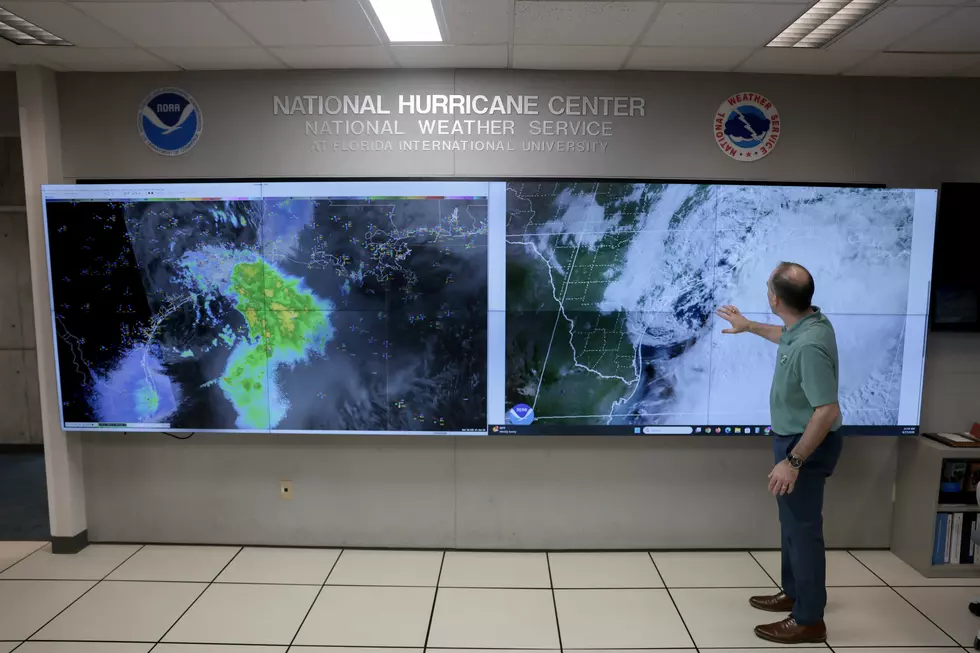









Failed requests
These URLs were requested, but there was no response received. You will also see them in the list above.
- Domain
- kpel965.com
- URL
- blob:https://kpel965.com/ae238523-ed14-4a06-8669-39a94d68d5c1
- Domain
- kpel965.com
- URL
- blob:https://kpel965.com/77317754-5d87-4219-8369-63501210b1d3
- Domain
- townsquare.media
- URL
- https://townsquare.media/site/36/files/2020/08/Untitled-design-5.jpg?w=980&q=75
Verdicts & Comments Add Verdict or Comment
88 JavaScript Window variables
Go Pro
Only in urlscan Pro
Inspect and pivot on JavaScript variables, identifiers, and other key site metadata data with urlscan Pro. Reveal and search on client-side frameworks, runtime variables, and custom values.
Click for more information
Free trials of urlscan Pro are available.
These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.
object| 0 object| 1 object| 2 object| 3 object| 4 object| 5 object| 6 object| 7 object| 8 object| TSM object| taskQ function| gtag object| dataLayer function| Osano object| webpackChunk_osano_cmp_consent_manager function| __gpp function| __tcfapi function| __uspapi object| apntag object| __permutive object| permutive object| googletag object| pbjs object| PushlySDK object| twttr object| ZERG function| fbLoaded number| PREBID_TIMEOUT boolean| REQUEST_BIDS_ON_PAGE_LOAD boolean| SHOW_ADS_ON_PAGE_LOAD object| pbjsChunk object| _pbjsGlobals object| pbjsBidderSettings object| apstag function| dealWithAlephCount object| __INITIAL_STATE__ object| bidLog function| admiral function| QS02NzNDRTAxNEUxRDM0NzQxN0JBREM3MEEtMTg object| __apEarlyQS02NzNDRTAxNEUxRDM0NzQxN0JBREM3MEEtMTg object| __apEarlyInstalled object| wpJsonRciWidget object| ua_result object| revcontent function| renderRCWidget object| e object| __bt_edge_data object| __bt object| __bt_intrnl boolean| __bt_already_invoked string| _PN_IDK_ object| _PN_IDC_ object| _PN_IPG_ object| PublisherCommonId object| __twttrll object| __twttr object| gapi object| ___jsl object| FB number| PIN_20705 object| __bt_tag_d object| litHtmlVersions object| ggeac object| google_tag_data object| google_js_reporting_queue object| webpackChunkexpressblog function| initCarbon object| globalActionCreators function| fbAsyncInit function| onYtEvent object| cQ object| google_reactive_ads_global_state function| dspCriteoRTUSCallback function| dspCMCallback object| google_tag_manager object| _sf_async_config function| 4dm1r11545242527 object| PIN_1788942916094 string| value object| key object| PinUtils object| instgrm function| onYouTubeIframeAPIReady object| webVitals function| sendToGTM string| aleph object| teads_analytics object| gaGlobal6 Cookies
Go Pro
Only in urlscan Pro
Review, search, and pivot on browser cookies and persistence site data to see how a site tracks users and keeps sessions alive across visits.
Click for more information
Free trials of urlscan Pro are available.
Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.
| Domain/Path | Expires | Name / Value | |||
|---|---|---|---|---|---|
| kpel965.com/ | 1970-01-21 19:05:18 |
Name: abgroup Value: B |
|||
| kpel965.com/ | 1970-01-21 16:55:44 |
Name: cogitoergosum Value: eyJsb2NhdGlvbiI6InVuZGVmaW5lZCx1bmRlZmluZWQiLCJ0aW1lc3RhbXAiOiJXZWQsIDA5IFNlcCAyMDI2IDA4OjM1OjE1IEdNVCJ9 |
|||
| kpel965.com/ | 1970-01-21 17:38:54 |
Name: connect.sid Value: s%3AdZq-015bqTY9M8LoUSF-NLPUpO0hyEDb.5JBpi5wCNhrr4WcyNbWkngQnPXHE7F1UMV6jkZr4%2F10 |
|||
| .twitter.com/ | 1970-01-21 16:55:44 |
Name: __cf_bm Value: R7mn4cp07stXx_yINjydEO4ikNq_XeezYVnF9lawswo-1788942915.9801967-1.0.1.1-XaP5Em7kUmvrFARjSI6LReOzMmdv3jegZIrRUoxk8cU_TUhu2Kp6aOqAimkI4HE_gyac8qeUb_nVwyqP1HYe_TNDmIon4SSk5DjYScXDlqslC1YjEYww0GuApCzADb5l |
|||
| cdn.production.townsquareblogs.com/ | 1970-01-22 01:41:18 |
Name: aleph Value: 56e90d98-4716-5923-aa2f-b6797dffd6d7 |
|||
| .kpel965.com/ | 1970-01-22 02:24:30 |
Name: _awl Value: 2.1788942916.5-90cbc6a18d9a7292ba39541335eb91b9-6763652d6575726f70652d7765737431-0 |
2 Console Messages
A page may trigger messages to the console to be logged. These are often error messages about being unable to load a resource or execute a piece of JavaScript. Sometimes they also provide insight into the technology behind a website.
| Source | Level | URL Text |
|---|
Security Headers
This page lists any security headers set by the main page. If you want to understand what these mean and how to use them, head on over to this page
| Header | Value |
|---|---|
| Strict-Transport-Security | max-age=31536000; includeSubDomains |
| X-Content-Type-Options | nosniff |
| X-Frame-Options | SAMEORIGIN |
Indicators
This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.
40ba8f49-f119-4c3e-8d3a-08e85c30ef88.edge.permutive.app
973thedawg.com
a.teads.tv
aax.amazon-adsystem.com
ab.dns-finder.com
acadianafirstalert.com
ad-delivery.net
ad.doubleclick.net
api.btloader.com
assets.pinterest.com
assets.revcontent.com
cadmus.script.ac
cdn.api.btloader.com
cdn.production.townsquareblogs.com
cmp.osano.com
driftingchef.com
fonts.googleapis.com
fonts.gstatic.com
images.unsplash.com
js-sec.indexww.com
k.p-n.io
kpel965.com
log.pinterest.com
pagead2.googlesyndication.com
platform.instagram.com
platform.twitter.com
region1.google-analytics.com
securepubads.g.doubleclick.net
static.teads.tv
syndication.twitter.com
townsquare.media
trends.revcontent.com
trendsp.revcontent.com
unpkg.com
www.googletagmanager.com
www.instagram.com
www.nhc.noaa.gov
yeet.revcontent.com
kpel965.com
townsquare.media
104.18.25.18
108.138.4.226
130.211.23.194
142.251.127.155
142.251.13.94
142.251.13.97
142.251.14.149
142.251.20.154
146.75.120.157
151.101.192.84
151.101.194.132
157.240.0.174
157.240.0.63
162.159.140.229
18.245.31.112
18.245.31.35
2001:4860:4802:34::36
216.152.143.250
23.207.210.138
2600:1901:0:ab09::1
2600:9000:275d:3200:0:bd73:4880:93a1
2606:4700:10::6814:2f50
2606:4700:10::ac42:ab85
2606:4700:4401::6812:291e
2606:4700::6812:116
2a00:1450:4001:c0f::61
2a00:1450:4001:c21::5f
2a02:26f0:2b80:2f::215:8f4f
2a02:26f0:7100::687e:2598
2a02:26f0:e300::215:2173
2a02:26f0:e300::215:2188
2a02:26f0:fa00::214:87a3
2a04:4e42:600::720
2a06:98c1:310d::ac40:98f3
3.174.46.116
3.248.137.33
34.110.146.185
34.36.200.111
54.170.116.67
65.9.130.110
98.91.154.91
0032eef6921445687ab7edd474360ea2788c2cabfb9ddfeaa339d5a5e46c2018
0579619786f40ef19b66506851c5d4a0e65b1d04212419bb8f9b14adac695f0c
095711c5ca605bbb63f3d20ae21767744efb09b53ff9ed3af86d898e5ea4cfde
0ab0ae1a219545415f5e31daccc3730231951bd262fc4727a36f42a70352fa25
0d0e16990472a4a44a3119ea7aef276be1acaf4788e5f52015bcae7cb9ef73ab
0dcefa0b117fa5dc44eefa92d2bf221f3455b29354cc940f144bb268100fc116
101ead936a2281d53dcc064b7e2a2ab0d53b92ef3ef7b34b668673007895c860
10a82b9e4c8e0ef58bb6a5ee3e205a1db86c4737051da5206a8b97531dfdf770
121161819087006bf46ff3e72b3f6918071c1b9a553527b051ae31aaef820caf
1322fedfbe2b6ded3774d02e2c91905329a4d35c6f9233e6d9a014f2d31f6684
1404ca348bd75ef836f4dd8b6f2cc719458642d1237c368296b2fc652dca47dc
14f23757c6b41b4b6c0b967ca3fa74ff47a868728158373461c4e6e4b6368f19
16052bdb4e4c0038ff632764573efda5a857ad100a89fa1a3c973d317ae472e1
1b48b1459b53e099a2ce43d0fdc459980c04cc7be0adda5e0d4b59e2514810e8
2208f61904a8bc6091124b41b378f3428cb8c81e5739bb99bb4921b0f91f03d6
22e6f6654c5f2d0052d08912175c657a73799d295382bd640954ab1a6fa44989
2689367b205c16ce32ed4200942b8b8b1e262dfc70d9bc9fbc77c49699a4f1df
26cff5228b7907626d8fdac6a48953093d8bd57a1595b96ac6ad76b48a5a6cad
2e667ce604bac9a16b97f29a9e98140e62403b198ce649486a016afa12cafcb9
2ee458c844d423e058db09bdc75089f1d1d03c3831c0bab6892e6e1a2cc4340b
2fc012dca1f07374d1e7f3448d5f1c674edb3a7f6bb1d47e1ce7d9d8d4838559
302da628a6afc3e93f1b86bf7c65e4d6536d8283d78266964822a76d1c645aa4
33c70c297b1a729f965a6aca60b7b3bb7a3b06bd13efe07698516fa98ac8b9f9
36bceb15ce0b3b7427dc1b983dd1386c4843ee5ade2df3548aa53dee33fc754c
37ec5817a0032426b8e9dd7991df9bc48d38d0b4ad358a8890dbe02fb92be13c
38e1e6c680ef39235e64726496ece6b39355e5fb5d2ff9f94881393427ef9d67
3c1e320f0506d1cb42d1b8dbfe017b9d30f58dd8f824ac8086a1c94671b09ab9
3eb10792d1f0c7e07e7248273540f1952d9a5a2996f4b5df70ab026cd9f05517
409031553e4d7b8882e8659ec5c217a3a63764fcb702613bad8fdbba197bbba1
435e2628ae499b22cbd9955abf98d409d9c321ba3e7bd0fa8d56e85ceff1534e
47d55fcfef3b47b3161f30f400dce523a4cc3805b16597758c6b9872cc117a8d
4880cf29442c881d8d8f5efa1e1d7be0fe04e94cd21e79343a3a6ef1376145ff
4b89ecb8d8ce5344c5cd84fe585d0d5c2664a9ba1d90e0b8da5445ef6d673102
4c56a3b1b15856ec2abc861dea0dcd9d64ad7c84aa6b2b934fd972e857d917e5
4d38b03ca20eea03243981adec2ee13bb78b5b86d7a2e46fb9837f93c6700ecc
5defb5463065618ffe0a5d0e81bff408dab5b1559dd546f169718eb0e9f44a2f
5e985a476fedf568835be8746a905079b7f10c5fc840f8af1e569a7bef531e2a
644297aa9b138b84d5aac17a169c20ea84e721bd4e871313ba0b62ffbfd37216
669441a7306cc560ad52a62c64d696c7ba42c3d56eff32291ecd7f7ab7f06342
66ffe114dda64d52da133343112afe983bee28056d60ec554fd4cc5d2cbf5bc8
6a67dbb7dfc71d5711bcc840ab6970c2e826e3260e5f67b7be780b7ef03990d1
70c00445d6632039ed99af760731daf3bf60eb12061863ee61e2cd7276a54d18
75ed714c577f52ce4ae064fa4a4f51c87b23266b3502d7e2035d63d465b7cfc5
7634f3be137ff76e5658e41c08c842f944d5c401d9d6b1b723ae315999bb5d74
79e9f1410dfcf6f141bae90a3c3195c275ec390f5d35fce5bcba4b4927a1a7e1
801cbab2e4afc0acbce199d547678458d79741ec9dede9166d8a8fb9e057ec88
81a8ab3a9fc9156757213c0dd190b3502f026bfbcf23ec254baaed045f85dae1
8d230115e58faa2ed303bee567b91d1a792e0c958a0118998b53648b2ab7c057
8f9ea68e6e3d17b22f328186ba4735c492578c3a2563a7b101f416d1bcf87f8f
9196f3b56c6a51be04742113acf6cc343ab44f2bf6f2ca75635e689adec5cb1c
9251a1c9d9d15d3906103e3fad910ff80a2f939accc93a6fa5d12220dba410fa
948cd6f56b9cef53de68689db069de90c7cd334d81c524bb035d428f5434e925
9e52aa0a71076e34d6e6d2a33e2c0f65049074c1004ab93a64921bbba0c9b4af
a1246500e54878521c20eaca060cdbff39b403619b4751d39bf8828246d51309
a26956630a43db8ec1eb8614c7092ca069911c82e0a6844a7bbf7d5a6dceb64e
a68c4f8f718c3d0b374349240a61da37d9b0984a7f16d6c6388e9b3fe50c5eb8
a7a53b98ddd8a9a40e23507bdced556b2bb56d7a738ac2fcfa31bcc3e0a75fc6
a7c828360391bee1c774c990e36a7449585ce19bab8a6714ba1370964a4b13ea
a93daf11605785fd4191ef6b9aa538901d6ae52fcda46e1b2e9f1db57eb6174e
ab0945d6ef230f15ecab7c396b3240f8798d5bf3a68e828e11eef2feb861ff5c
ae04f21df7a1cfb61b84372097cdf70a5ec9f71b66ff2945ac5f5edb8c8ff533
b3024518138a543968ec29b9965ffb5ba965d00184e664db1b385384933064ec
b372d64a2906ed090b515a4c0d08166577ab102b65a1624299005f3c50e1d2fd
b38378072c29e3988c868f560b7233837a9a354e64e13f5b3db5b50abed897c6
b8fca4f3fa5a78a64b300c052e8a7caff39ffa2f8e2f3ed9a37fbbcffd2892db
ba6f96523500534b16b83dee795696eaf04a397b257cd465f928e37faca918ca
bf0bcd39da75aa2ecad630a53a4a2deee15c401be87c93a3b5369fddef6cfae1
c072dbb630d4e992682f0c7d9ce5caf9600cd3320747e5124675978e49c9088a
c2d785e090ca7d23d106aaf8c9eb48e17c28b7d9273f2b609de5eb9deed0cefd
c4a86b616c90834b14c53baafb790b41111bbca30f66ef50f7e2afe2c05c6ad5
c630415b80c0fd1a865b4dc8a851387c4b8eb1b6d997f89769ed0682fe78653a
cda0857662d80af528315ae21ae76ca58c3fb11a32d5f3ed0745c419ca68a94d
cf4724b2f736ed1a0ae6bc28f1ead963d9cd2c1fd87b6ef32e7799fc1c5c8bda
d2b1c25ef44938c44a908a93e143ca16c30231a4f49c9cad29621d451f3c6441
d961b08e4321250926de6f79087594975fe20ad1518de8f91eb711af5d1a6ef8
d9fdd5d68e2e00381506d671e9ba8d284320ad70f19c2ee5d0ce2e1ac4317463
da0a1f508ae784daa5035f445d428a5f8c0e586bcc6f5f783927cbea57166252
dafca659298a2f28dc3ca35f02a5ef6444fd9f6e1ef044894c13bfbfdf4f2530
e2aed6db07c6b687f00b176a1d672010faad42aecf45a4251c9184e07ccabf5f
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
e5efccf44b301b5550c3fe8e5b9802449a5680e25d1f7885a56cbb62e244fa45
ec99e42912e1015c96f2dd9ab555c271801e6e76e9539229ce60f5191b939269
ed9d15f78cbaac9b62cf7744d7e65432f4e4af4c492a8999dac90fb3f976f7e9
f1d555bcb983305090a9a8025319e9de7f7127a684c442045c0c2adafea9b876
f3b6813b25d5b3fb92fa145c68dcb8e7f3987e1cf5305fad589ff546b823c534
f545d215fc31612e5d8f9eadf67793d9d79a4b722c318dea5dabc3452d46ced9
f759996a85b1ddf539ef3f16fdca3d39e48f670aef69e82c6200cc2b5f9f47bd
f76466476152b1666786365b73a6f974cd323e435d1c5fba26c1247efe9bd0e8
f8fac69e0db10a87e3e05122097ad89d3ebe4cbbf2337f480ef5feb505c771f6
f99b7b69017b94d55f29ea5506dfe7b5c7439b1830519e39bedd89bd9e0630df
fa6f38ec6c56a27a4744130b2f6c2b1f6163a44c7cd0381922cbdcd6d8a0b24d
fb6808b7e654821ce2c59576b4efe541c53841a882d98925f1e43e4eecec6bba