
mallogram.com
172.67.163.120
Public Scan
Open in
urlscan Pro
https://mallogram.com/ 7yr old
Submission: On September 11 via api (September 11th 2026, 7:02:29 am UTC) from ID — Scanned from CA Go Pro
Only in urlscan Pro
- Select different country locations for Private Scans.
- Use a global network of additional scanning locations and residential IPs for scanning.
- Interact with pages while you are scanning them.
- Download files from remote websites.
- Scan websites on the Tor Network.
Summary
TLS certificate: Issued by YE2 on September 10th 2026. Valid for: 3mo.
This is the only time mallogram.com was scanned on urlscan.io!
urlscan.io Verdict: No classification
Domain & IP information
| IP Address | AS Autonomous System | ||
|---|---|---|---|
| 2 | 172.67.163.120 172.67.163.120 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 7 | 207.174.26.219 207.174.26.219 | 26548 (PUREVOLTA...) (PUREVOLTAGE-INC - PureVoltage Hosting Inc.) | |
| 6 | 3.162.3.125 3.162.3.125 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 7 | 3.162.7.132 3.162.7.132 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 1 | 172.67.69.232 172.67.69.232 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 4 | 104.21.59.246 104.21.59.246 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 13.225.196.19 13.225.196.19 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 8 | 104.16.80.73 104.16.80.73 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 36 | 8 |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| mallogram.com 7yr old |
ASN26548 (PUREVOLTAGE-INC - PureVoltage Hosting Inc., US)
| i.ibb.co 8yr old | |
| i.ibb.co.com 3yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-3-162-3-125.yul62.r.cloudfront.net
| d2ati23fc66y9j.cloudfront.net 7yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-3-162-7-132.yul62.r.cloudfront.net
| d24epxax9d77vm.cloudfront.net 2yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| logos-world.net 7yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| imgstore.io 6yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-13-225-196-19.yul62.r.cloudfront.net
| www.ubuy.com.kh 5yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| static.cloudflareinsights.com 7yr old |
| Apex Domain Subdomains |
Transfer | |
|---|---|---|
| 13 |
cloudfront.net
d2ati23fc66y9j.cloudfront.net — Cisco Umbrella Rank: 176372 7yr old d24epxax9d77vm.cloudfront.net — Cisco Umbrella Rank: 197792 2yr old |
658 KB |
| 8 |
cloudflareinsights.com
static.cloudflareinsights.com — Cisco Umbrella Rank: 307 7yr old |
59 KB |
| 5 |
co.com
i.ibb.co.com — Cisco Umbrella Rank: 95495 3yr old |
60 KB |
| 4 |
imgstore.io
imgstore.io — Cisco Umbrella Rank: 55507 6yr old |
10 KB |
| 2 |
ibb.co
i.ibb.co — Cisco Umbrella Rank: 10925 8yr old |
309 KB |
| 2 |
mallogram.com
mallogram.com 7yr old |
115 KB |
| 1 |
ubuy.com.kh
www.ubuy.com.kh — Cisco Umbrella Rank: 281894 5yr old |
7 KB |
| 1 |
logos-world.net
logos-world.net — Cisco Umbrella Rank: 122641 7yr old |
3 KB |
| 36 | 8 |
| Domain | Requested by | |
|---|---|---|
| 8 | static.cloudflareinsights.com |
mallogram.com
|
| 7 | d24epxax9d77vm.cloudfront.net |
mallogram.com
|
| 6 | d2ati23fc66y9j.cloudfront.net |
mallogram.com
|
| 5 | i.ibb.co.com |
mallogram.com
|
| 4 | imgstore.io |
mallogram.com
|
| 2 | i.ibb.co |
mallogram.com
|
| 2 | mallogram.com |
static.cloudflareinsights.com
|
| 1 | www.ubuy.com.kh |
mallogram.com
|
| 1 | logos-world.net |
mallogram.com
|
| 36 | 9 |
This site contains links to these domains. Also see Links.
| Domain |
|---|
| amp-duit8-mallogram.pages.dev |
| www.ubuy.hk |
| www.ubuy.co.in |
| www.ubuy.co.id |
| www.u-buy.jp |
| www.ubuy.com.my |
| www.ubuy.mv |
| www.ubuy.com.ph |
| ubuy.com |
| ubys.us |
| Subject Issuer | Validity | Valid | |
|---|---|---|---|
| mallogram.com YE2 |
2026-09-10 - 2026-12-09 |
3mo | crt.sh |
| ibb.co YE1 |
2026-08-12 - 2026-11-10 |
3mo | crt.sh |
| *.cloudfront.net Amazon RSA 2048 M04 |
2026-08-25 - 2027-03-10 |
7mo | crt.sh |
| logos-world.net WE1 |
2026-08-06 - 2026-11-04 |
3mo | crt.sh |
| imgstore.io WE1 |
2026-08-31 - 2026-11-29 |
3mo | crt.sh |
| ubuy.co.it Amazon RSA 2048 M04 |
2026-07-19 - 2027-02-01 |
7mo | crt.sh |
| cloudflareinsights.com WE1 |
2026-08-14 - 2026-11-12 |
3mo | crt.sh |
This page contains 1 frames:
Primary Page:
https://mallogram.com/
Frame ID: 92F17419FECE8B3C3A8979BB756C70EA
Requests: 36 HTTP requests in this frame
Screenshot
Go Pro
Only in urlscan Pro
Use the Visual Search feature to find pages with visually similar screenshots.
Click for more information
Free trials of urlscan Pro are available.
Page Title
DUIT8 | APK Slot Online Resmi dan Terpercaya di Indonesia 2026Detected technologies
 WordPress
(CMS)
Expand
Detected patterns
- /wp-(?:content|includes)/
 AMP
(JavaScript frameworks)
Expand
Detected patterns
- <link rel="amphtml"
 Cloudflare Browser Insights
(Analytics)
Expand
Detected patterns
- static\.cloudflareinsights\.com/beacon(?:\.min)?\.js
Page Statistics
10 Outgoing links
Go Pro
Only in urlscan Pro
Effortlessly use any on-page link as a pivot to discover other pages pointing to the exact same destination. Seamlessly trace both specific URLs and broader domains to uncover hidden connection networks and map out backlink relationships with ease.
Click for more information
Free trials of urlscan Pro are available.
These are links going to different origins than the main page.
Title: LOGIN
Search URL Search Domain Scan URL
Title: Hong Kong
Search URL Search Domain Scan URL
Title: India
Search URL Search Domain Scan URL
Title: Indonesia
Search URL Search Domain Scan URL
Title: Japan
Search URL Search Domain Scan URL
Title: Malaysia
Search URL Search Domain Scan URL
Title: Maldives
Search URL Search Domain Scan URL
Title: Philippines
Search URL Search Domain Scan URL
Title: View All Countries
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Redirected requests
There were HTTP redirect chains for the following requests:
36 HTTP transactions
Go Pro
Only in urlscan Pro
Inspect WebSocket connections, examine POST data effortlessly, and track overlap counts in real time. Features live search and filtering across all HTTP output, complete with full response metadata for deep analysis.
Click for more information
Free trials of urlscan Pro are available.
0 data transactions
| Method Protocol |
Status | Resource Path |
Size x-fer |
Time Latency |
Type MIME-Type |
IP Location |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
|
GET H3 |
200 |
Primary Request
/
Show response
mallogram.com/ |
617 KB 114 KB |
1054ms
997ms |
Document
text/html |
172.67.163.120 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
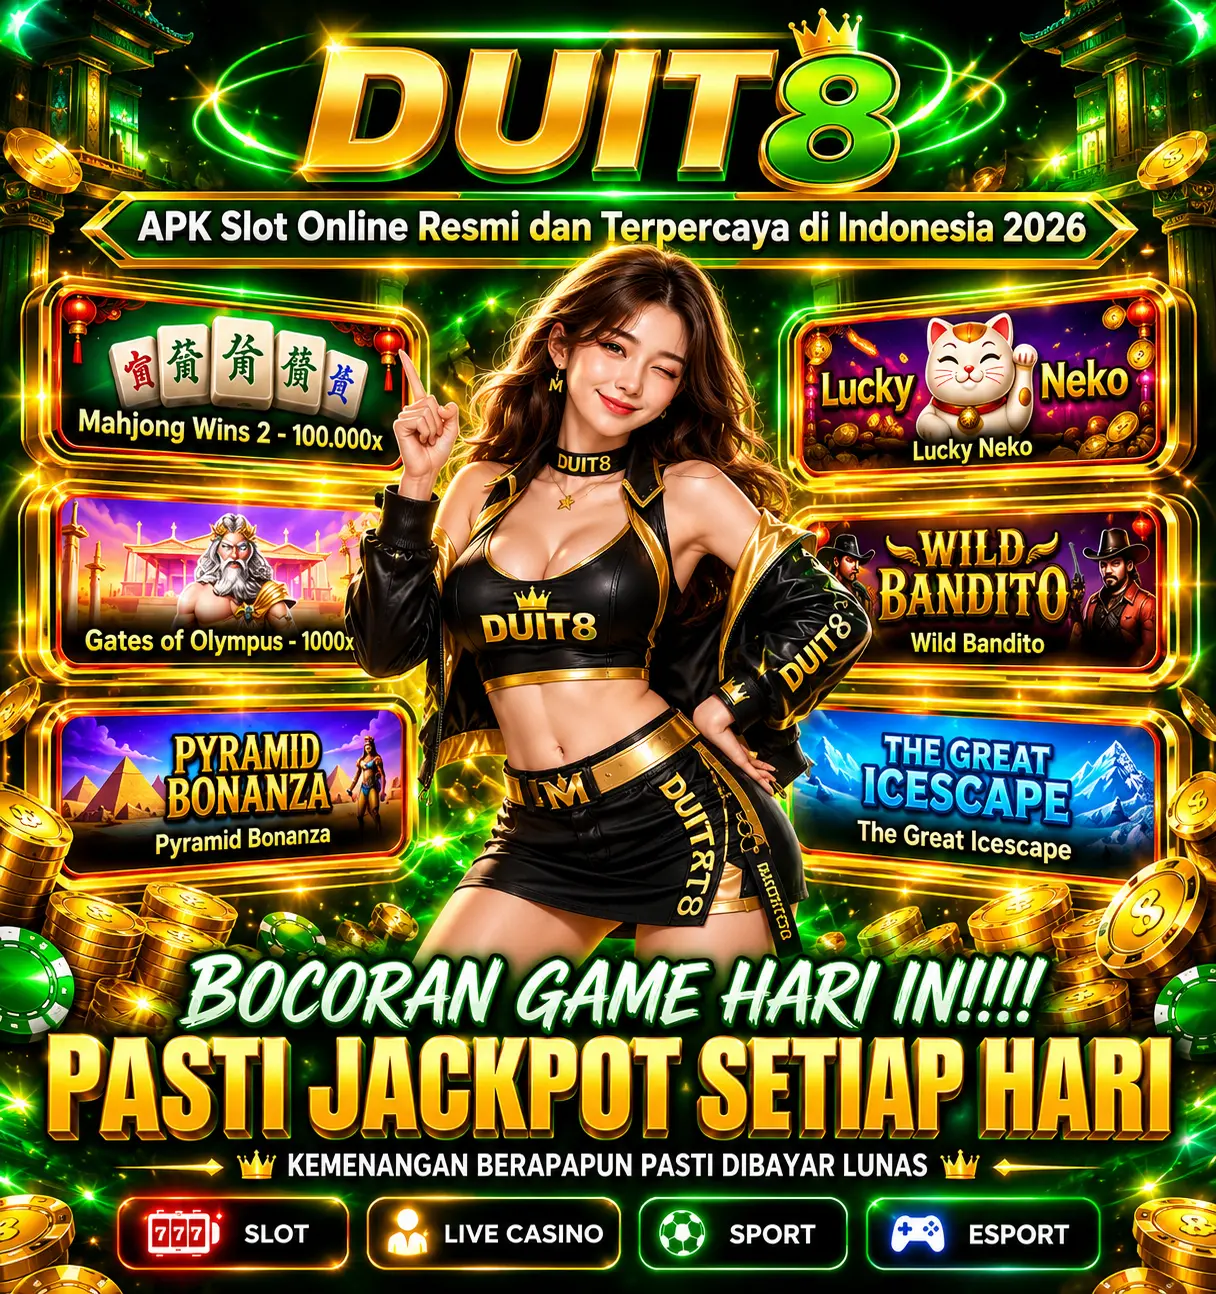
banner-duit8-11-09-2026.webp
i.ibb.co/nsDqpbc3/ |
308 KB 309 KB |
168ms
63ms |
Image
image/webp |
207.174.26.219 PureVoltage Hosti... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
explore-icon.svg
d2ati23fc66y9j.cloudfront.net/ubuycom/assets/v5/images/ |
403 B 795 B |
301ms
34ms |
Image
image/svg+xml |
3.162.3.125 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
logo-duit8-11-09-2026.png
i.ibb.co.com/ZzVTD2DV/ |
59 KB 59 KB |
105ms
91ms |
Image
image/png |
207.174.26.219 PureVoltage Hosti... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
homepage-sprite.webp
d2ati23fc66y9j.cloudfront.net/sprite-img/ |
156 KB 156 KB |
281ms
41ms |
Image
image/webp |
3.162.3.125 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
poppins-semibold.woff2
d24epxax9d77vm.cloudfront.net/ubuycom/assets/v5/fonts/poppins-webfont/ |
51 KB 51 KB |
319ms
89ms |
Font
font/woff2 |
3.162.7.132 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
poppins-regular.woff2
d24epxax9d77vm.cloudfront.net/ubuycom/assets/v5/fonts/poppins-webfont/ |
51 KB 52 KB |
333ms
104ms |
Font
font/woff2 |
3.162.7.132 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
fa-solid-900.woff2
d24epxax9d77vm.cloudfront.net/ubuycom/assets/v5/fonts/poppins-webfont/ |
110 KB 111 KB |
269ms
40ms |
Font
font/woff2 |
3.162.7.132 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
banner-duit8-11-09-2026.webp
i.ibb.co/nsDqpbc3/ |
308 KB 0 |
0ms
0ms |
Image
image/webp |
207.174.26.219 PureVoltage Hosti... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
favicon-duit8-11-09-2026.webp
i.ibb.co.com/PGG6nSX7/ |
1 KB 2 KB |
48ms
42ms |
Image
image/webp |
207.174.26.219 PureVoltage Hosti... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Visa-Logo-120x67.png
logos-world.net/wp-content/uploads/2020/05/ |
2 KB 3 KB |
219ms
34ms |
Image
image/png |
172.67.69.232 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
qris.webp
imgstore.io/images/2025/03/19/ |
654 B 1 KB |
230ms
46ms |
Image
image/webp |
104.21.59.246 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
bca.webp
imgstore.io/images/2025/03/19/ |
768 B 1 KB |
228ms
46ms |
Image
image/webp |
104.21.59.246 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
ovo.webp
imgstore.io/images/2025/03/19/ |
786 B 1 KB |
226ms
43ms |
Image
image/webp |
104.21.59.246 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
mandiri.png
imgstore.io/images/2025/12/20/ |
6 KB 7 KB |
229ms
46ms |
Image
image/png |
104.21.59.246 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
payment_methods-175369014491.png
d2ati23fc66y9j.cloudfront.net/ubuycom/homebanner/ |
2 KB 2 KB |
169ms
104ms |
Image
image/png |
3.162.3.125 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
payment_methods-175368113152.png
d2ati23fc66y9j.cloudfront.net/ubuycom/homebanner/ |
4 KB 5 KB |
170ms
106ms |
Image
image/png |
3.162.3.125 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
payment_methods-175368114244.png
d2ati23fc66y9j.cloudfront.net/ubuycom/homebanner/ |
4 KB 4 KB |
169ms
105ms |
Image
image/png |
3.162.3.125 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
loading.gif
d2ati23fc66y9j.cloudfront.net/ubuycom-v1/images/ |
24 KB 25 KB |
156ms
96ms |
Image
image/gif |
3.162.3.125 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
poppins-medium.woff2
d24epxax9d77vm.cloudfront.net/ubuycom/assets/v5/fonts/poppins-webfont/ |
50 KB 51 KB |
111ms
107ms |
Font
font/woff2 |
3.162.7.132 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
fa-brands-400.woff2
d24epxax9d77vm.cloudfront.net/ubuycom/assets/v5/fonts/poppins-webfont/ |
99 KB 99 KB |
129ms
125ms |
Font
font/woff2 |
3.162.7.132 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
poppins-bold.woff2
d24epxax9d77vm.cloudfront.net/ubuycom/assets/v5/fonts/poppins-webfont/ |
50 KB 51 KB |
115ms
112ms |
Font
font/woff2 |
3.162.7.132 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
poppins-extraBold.woff2
d24epxax9d77vm.cloudfront.net/ubuycom/assets/v5/fonts/poppins-webfont/ |
49 KB 50 KB |
124ms
121ms |
Font
font/woff2 |
3.162.7.132 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
custom.js
Show response
www.ubuy.com.kh/ubuycom/assets/v5/custom_js/ |
24 KB 7 KB |
309ms
48ms |
Script
application/javascript |
13.225.196.19 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
vcd15cbe7772f49c399c6a5babf22c1241717689176015
Show response
static.cloudflareinsights.com/beacon.min.js/ |
19 KB 7 KB |
232ms
75ms |
Script
text/javascript |
104.16.80.73 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
v8c78df7c7c0f484497ecbca7046644da1771523124516
Show response
static.cloudflareinsights.com/beacon.min.js/ |
30 KB 11 KB |
211ms
55ms |
Script
text/javascript |
104.16.80.73 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
v833ccba57c9e4d2798f2e76cebdd09a11778172276447
Show response
static.cloudflareinsights.com/beacon.min.js/ |
32 KB 11 KB |
187ms
31ms |
Script
text/javascript |
104.16.80.73 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
v4513226cdae34746b4dedf0b4dfa099e1781791509496
Show response
static.cloudflareinsights.com/beacon.min.js/ |
31 KB 11 KB |
218ms
62ms |
Script
text/javascript |
104.16.80.73 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
v3d52b47920f24c319d37e2661827c42b1787588026925
Show response
static.cloudflareinsights.com/beacon.min.js/ |
28 KB 9 KB |
205ms
49ms |
Script
text/javascript |
104.16.80.73 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
v31edd6df95cf4e85bb4c19e7a9bdbcba1788362987495
Show response
static.cloudflareinsights.com/beacon.min.js/ |
30 KB 10 KB |
185ms
30ms |
Script
text/javascript |
104.16.80.73 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
favicon-duit8-11-09-2026.webp
i.ibb.co.com/PGG6nSX7/ |
1 KB 0 |
1ms
1ms |
Image
image/webp |
207.174.26.219 PureVoltage Hosti... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
v833ccba57c9e4d2798f2e76cebdd09a11778172276447
Show response
static.cloudflareinsights.com/beacon.min.js/ |
32 KB 0 |
1ms
1ms |
Script
text/javascript |
104.16.80.73 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
v4513226cdae34746b4dedf0b4dfa099e1781791509496
Show response
static.cloudflareinsights.com/beacon.min.js/ |
31 KB 0 |
0ms
0ms |
Script
text/javascript |
104.16.80.73 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
404 |
rum
Show response
mallogram.com/cdn-cgi/ |
151 B 637 B |
26ms
24ms |
XHR
text/html |
172.67.163.120 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
favicon-duit8-11-09-2026.webp
i.ibb.co.com/PGG6nSX7/ |
1 KB 0 |
0ms
0ms |
Other
image/webp |
207.174.26.219 PureVoltage Hosti... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
favicon-duit8-11-09-2026.webp
i.ibb.co.com/PGG6nSX7/ |
1 KB 0 |
0ms
0ms |
Other
image/webp |
207.174.26.219 PureVoltage Hosti... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||








Verdicts & Comments Add Verdict or Comment
42 JavaScript Window variables
Go Pro
Only in urlscan Pro
Inspect and pivot on JavaScript variables, identifiers, and other key site metadata data with urlscan Pro. Reveal and search on client-side frameworks, runtime variables, and custom values.
Click for more information
Free trials of urlscan Pro are available.
These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.
function| fetchData function| getCartData function| changeStoreEvent function| updateCurrentStoreNode function| exploreGtmEvent function| moveToTop string| gtm_device number| timeout function| loadGtm function| showLoaderImage function| hideLoaderImage function| showLoaderImageAbs function| hideLoaderImageAbs function| showDotLoader function| hideDotLoader function| showDivLoader function| hideDivLoader function| serializeSearchUrl function| scrollFunction function| newsletter_submit function| newsletterLoaderShow function| newsletterLoaderHide function| storeModalClose function| createCookie function| readCookie function| copyToClipboard function| ubaAddtoWishlist function| success_flash_message function| error_flash_message function| showMcartLoader function| hideMcartLoader function| show_cart_popup function| get_cart_items function| maxLengthCheck function| spinner function| addSpinner function| setSortByFilterText function| removeFilterSidebarMobile function| objectValues function| showMoreFilter string| gogole_http_referer object| __cfBeacon0 Cookies
Go Pro
Only in urlscan Pro
Review, search, and pivot on browser cookies and persistence site data to see how a site tracks users and keeps sessions alive across visits.
Click for more information
Free trials of urlscan Pro are available.
Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.
1 Console Messages
A page may trigger messages to the console to be logged. These are often error messages about being unable to load a resource or execute a piece of JavaScript. Sometimes they also provide insight into the technology behind a website.
| Source | Level | URL Text |
|---|
Indicators
This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.
d24epxax9d77vm.cloudfront.net
d2ati23fc66y9j.cloudfront.net
i.ibb.co
i.ibb.co.com
imgstore.io
logos-world.net
mallogram.com
static.cloudflareinsights.com
www.ubuy.com.kh
104.16.80.73
104.21.59.246
13.225.196.19
172.67.163.120
172.67.69.232
207.174.26.219
3.162.3.125
3.162.7.132
08c4fd72f9d96a7aa554510dff2c293973b1b092dff1b9b282bce9111b50ef41
10dc5d611f07b1c57bccdfb7540e2ef4a15ce512a7f99c7069b9b39f4e2ecba5
1fb2859e054d0780a970f2fba01bc914944bafea1d04556e97e8487beeda78b4
2a84ae47aa8183257edf08360986803a809a2ea0c34c3c7229562c62c15c9ff2
2b12a2718379e49ed07ec90351a500f24a9d483c5ac86b983e4084f4c5ef3817
3424533d1f8cb2a6903d2c6c2c1c81937bdee61ed70b625dc81ec694bb35878c
41d5d03ceeb170744c16898a12efa43067d84d40dd76104a11e22e712134d715
4af01109aeb4ce73f1ee596f5cc7cd6ce2def6c5a0249127c941654a52862468
4b77eae349a8cbcea7133cf3640a64ebf1f69d54d8f6469d7be6fdc188ca4ca4
4bd0925efb7c7cf94942e1d74eb36e5c75e4cc84cfe9a0dfc950abc065f4ee92
4d4b447c3b4a45dcbc496bb678eda1409f8f76f74de9216b3c40f688cf16c261
56c67de04f49e052842e54a80af3a0499773be148cae5008ae141529324e2ac9
7c7fd857ca3716d26140f5d92d13cea81fbe9661c7d51caff16f0935e6ce3713
8a18d13015336bc184819a5a768447462202ef3105ec511bf42ed8304a7ed94f
a15dc4d20bb5e2c42fc64f6d3c0279ccee552ad23fdddeaaae97c34058e20060
a288b58f2364e3b318277c20f4aa96889b875bf2595776ba3a0c1adc800c2d3c
a7415a2d91793d8fc95e2109a53bac7c95d462b02b4114b64f7ad792148eabc3
aca73fc574e12740e3368860b88a284d01b643456f3ed6a06322ecb47750563f
c0b0b7afc6a894b48b1ba3e8373639b5e715af1f597ce8e54e7180761c3ebacb
c37d9916c146dbd96933d70c9fbbea62d94838bf86b77d0b7548e5b6d6606508
c72a01f23e3fcefa8e3640a48d7f6e73898510bf53cff898b48e73b3a753a898
d24bff547a8b87e585e5766c3162c50942db73b20da413fa96013a81f669b273
d66dd0f2f24c4343661a5396e1ba76782fe651f7d422209eded956ebf90900fc
df168feaaf3ac9457adcbeb0bf50cecb05ef7685b5c3dd41ca7fd969ddf0bf07
e1ac4849b9d4a498b68f8aca01e6ed99a11d94b35a2cec533b3916b8fb722fd6
ed266825df2ff85cc4f27593f50f15249848b8464712bb4371e9b7566b007f92
f1ff3447b57c8efa9dd9060d763592539b5f45bbbd8457e4cb18ae8e634de720
f3e741f7fd43de8c1ae0922bc83e996f4325562b739548cfd73708c3369cea83
f8b83fa1e35d2a2810cd48975ce3126b917ae9bada8b18ca7def5c10f23bde7b
fa785d18889e3276385e6b987178c247d07bd699bc29da9cda2f6bf33628ad1e