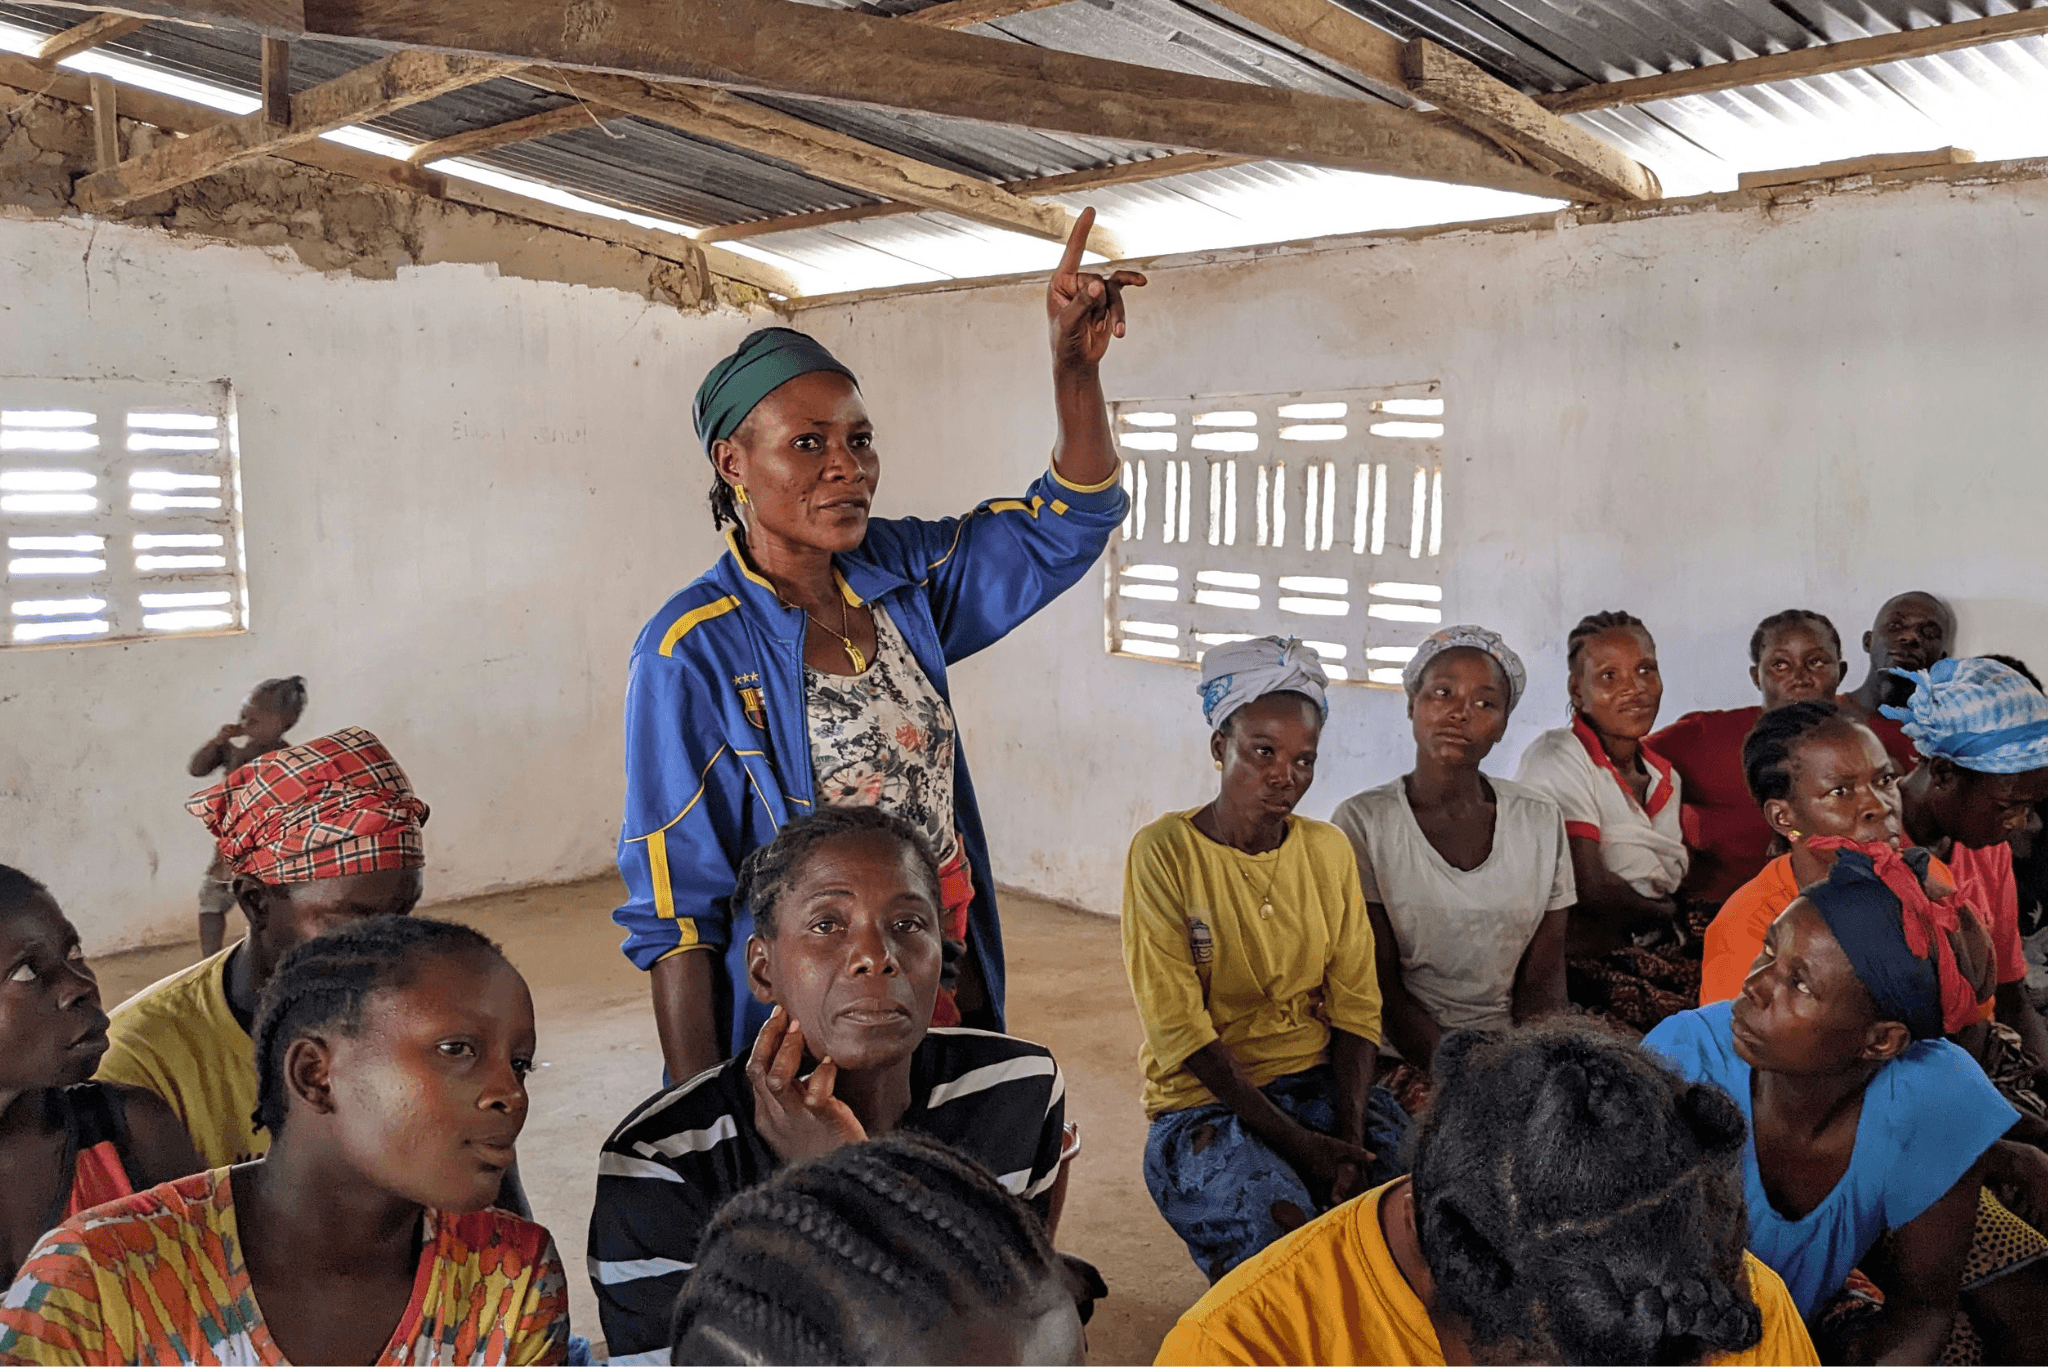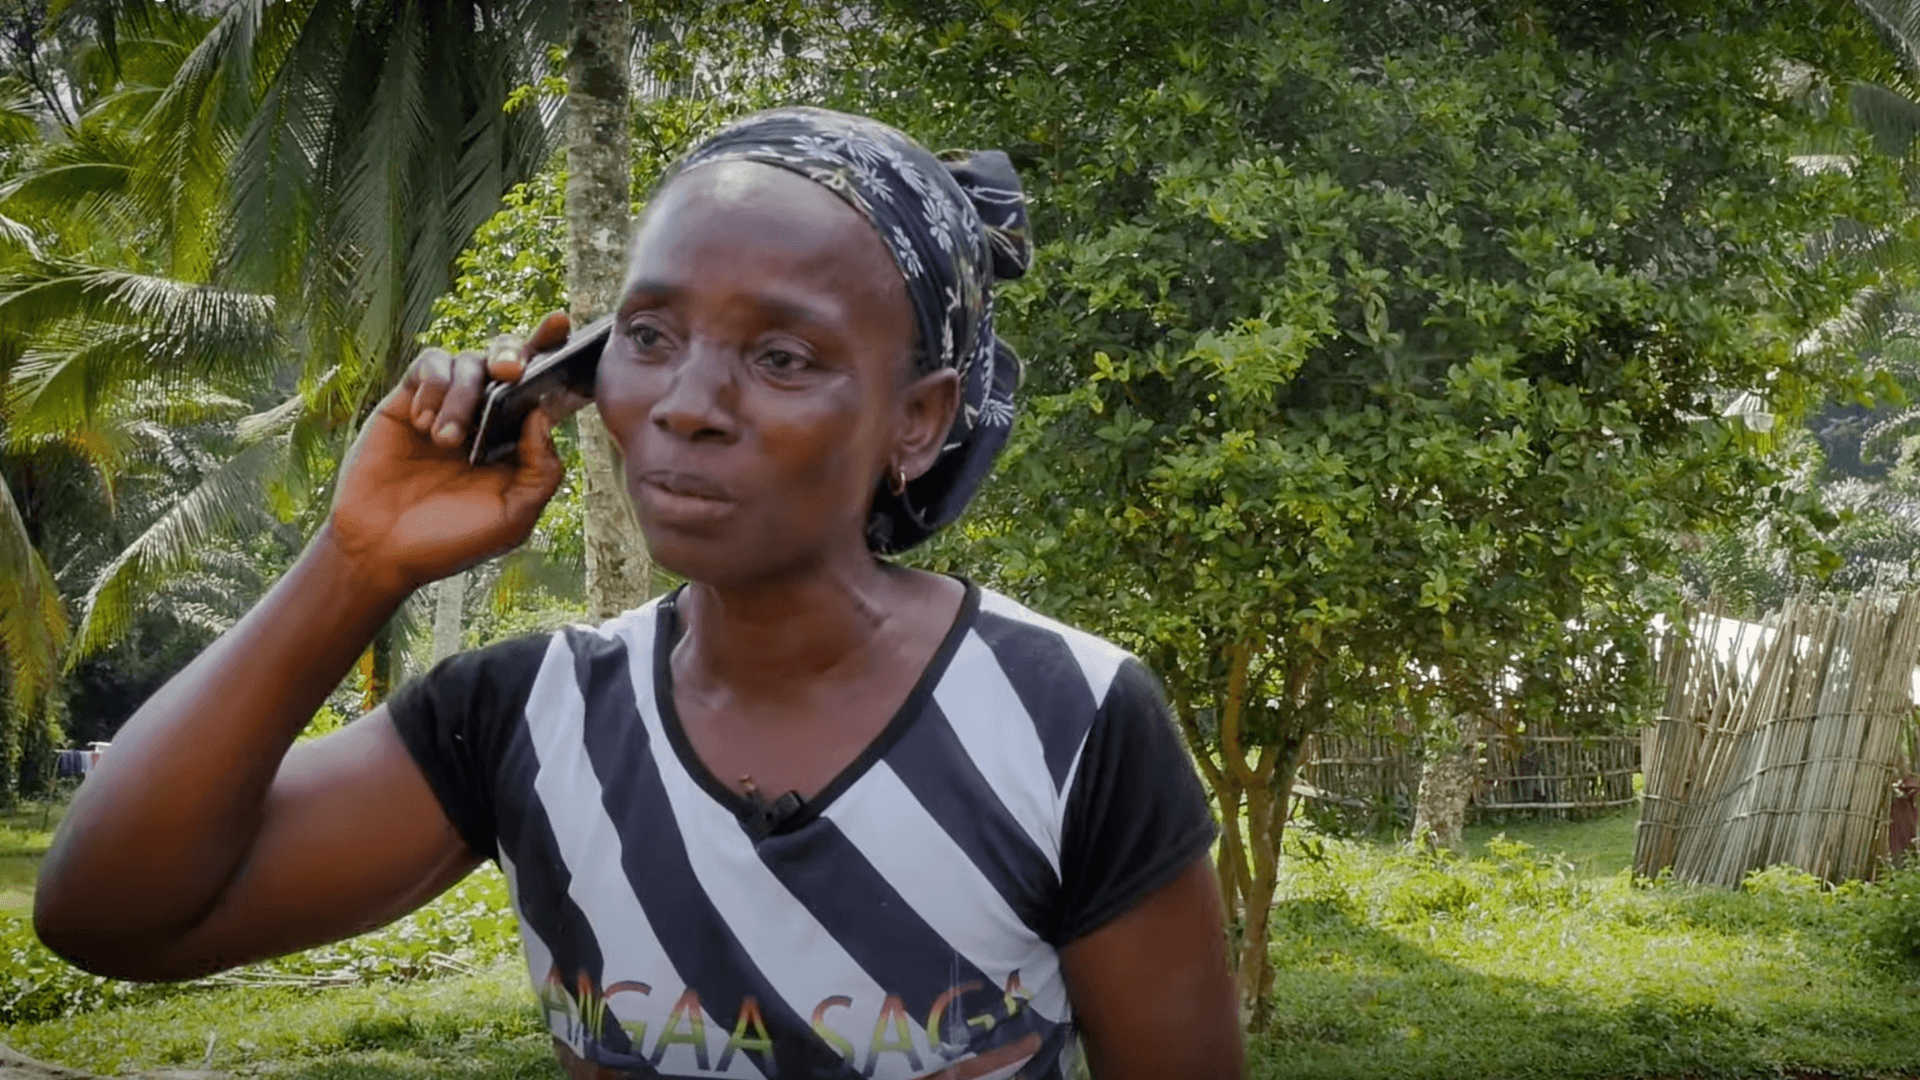Submitted URL:
http://www.educationliberia.org/ 24d old
Effective URL:
https://www.givedirectly.org/liberia 9yr old
Submission: On September 12 via api (September 12th 2026, 12:32:10 pm UTC) from US — Scanned from US

Summary

This website contacted 33 IPs in 2 countries across 19 domains to perform 109 HTTP transactions. The main IP is 13.35.78.128, located in United States and belongs to AMAZON-02 - Amazon.com, Inc., US. The main domain is www.givedirectly.org. 9yr old
TLS certificate: Issued by Amazon RSA 2048 M04 on August 24th 2026. Valid for: 7mo.
This is the only time www.givedirectly.org was scanned on urlscan.io!

urlscan.io Verdict: No classification

Domain & IP information

IP Address AS Autonomous System
1 1 52.216.10.178 52.216.10.178 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
2 42 13.35.78.128 13.35.78.128 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
4 23.215.0.145 23.215.0.145 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.)
1 142.251.163.95 142.251.163.95 15169 (GOOGLE) (GOOGLE - Google LLC)
1 3.171.38.13 3.171.38.13 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 192.178.155.95 192.178.155.95 15169 (GOOGLE) (GOOGLE - Google LLC)
1 23.215.0.138 23.215.0.138 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.)
2 142.251.179.97 142.251.179.97 15169 (GOOGLE) (GOOGLE - Google LLC)
7 3.167.69.84 3.167.69.84 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
11 142.251.153.4 142.251.153.4 15169 (GOOGLE) (GOOGLE - Google LLC)
3 142.250.31.94 142.250.31.94 15169 (GOOGLE) (GOOGLE - Google LLC)
1 18.238.49.55 18.238.49.55 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
2 23.55.176.231 23.55.176.231 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.)
2 57.144.70.128 57.144.70.128 32934 (FACEBOOK) (FACEBOOK - Facebook)
2 69.147.92.11 69.147.92.11 14777 (YAHOO) (YAHOO - Yahoo Holdings Inc.)
5 142.251.151.119 142.251.151.119 15169 (GOOGLE) (GOOGLE - Google LLC)
1 192.178.218.148 192.178.218.148 15169 (GOOGLE) (GOOGLE - Google LLC)
2 142.251.163.113 142.251.163.113 15169 (GOOGLE) (GOOGLE - Google LLC)
1 192.178.155.154 192.178.155.154 15169 (GOOGLE) (GOOGLE - Google LLC)
1 142.251.167.155 142.251.167.155 15169 (GOOGLE) (GOOGLE - Google LLC)
1 2 142.251.167.157 142.251.167.157 15169 (GOOGLE) (GOOGLE - Google LLC)
1 172.253.139.148 172.253.139.148 15169 (GOOGLE) (GOOGLE - Google LLC)
4 142.251.157.119 142.251.157.119 15169 (GOOGLE) (GOOGLE - Google LLC)
1 57.144.70.1 57.144.70.1 32934 (FACEBOOK) (FACEBOOK - Facebook)
1 172.253.62.119 172.253.62.119 15169 (GOOGLE) (GOOGLE - Google LLC)
3 5 104.18.41.41 104.18.41.41 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
1 192.178.155.132 192.178.155.132 15169 (GOOGLE) (GOOGLE - Google LLC)
1 192.179.24.94 192.179.24.94 15169 (GOOGLE) (GOOGLE - Google LLC)
2 172.217.114.4 172.217.114.4 15169 (GOOGLE) (GOOGLE - Google LLC)
1 54.160.143.175 54.160.143.175 14618 (AMAZON-AES) (AMAZON-AES - Amazon.com)
2 3.171.38.19 3.171.38.19 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
2 151.101.0.176 151.101.0.176 54113 (FASTLY) (FASTLY - Fastly)
1 44.232.203.244 44.232.203.244 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
109 33
Apex Domain
Subdomains
Transfer
50 givedirectly.org 2 redirects
www.givedirectly.org 9yr old
erinaceus.givedirectly.org 8mo old
donate.givedirectly.org 7yr old
3 MB
15 youtube.com
www.youtube.com — Cisco Umbrella Rank: 108 10yr old
1 MB
7 google.com
www.google.com — Cisco Umbrella Rank: 3 14yr old
analytics.google.com — Cisco Umbrella Rank: 143 9yr old
24 KB
6 doubleclick.net 1 redirects
ad.doubleclick.net — Cisco Umbrella Rank: 128 10yr old
stats.g.doubleclick.net — Cisco Umbrella Rank: 156 10yr old
googleads.g.doubleclick.net — Cisco Umbrella Rank: 66 10yr old
static.doubleclick.net — Cisco Umbrella Rank: 285 10yr old
4 KB
5 linkedin.com 3 redirects
px.ads.linkedin.com — Cisco Umbrella Rank: 403 9yr old
www.linkedin.com — Cisco Umbrella Rank: 807 14yr old
3 KB
5 typekit.net
use.typekit.net — Cisco Umbrella Rank: 562 14yr old
p.typekit.net — Cisco Umbrella Rank: 687 14yr old
86 KB
4 gstatic.com
fonts.gstatic.com — Cisco Umbrella Rank: 29 10yr old
www.gstatic.com — Cisco Umbrella Rank: 8 10yr old
111 KB
4 stripe.com
js.stripe.com — Cisco Umbrella Rank: 1295 13yr old
m.stripe.com — Cisco Umbrella Rank: 1356 10yr old
255 KB
4 googleapis.com
fonts.googleapis.com — Cisco Umbrella Rank: 43 10yr old
ajax.googleapis.com — Cisco Umbrella Rank: 617 10yr old
jnn-pa.googleapis.com — Cisco Umbrella Rank: 343 5yr old
32 KB
2 stripe.network
m.stripe.network — Cisco Umbrella Rank: 1439 9yr old
15 KB
2 yimg.com
s.yimg.com — Cisco Umbrella Rank: 1147 14yr old
7 KB
2 facebook.net
connect.facebook.net — Cisco Umbrella Rank: 224 14yr old
187 KB
2 licdn.com
snap.licdn.com — Cisco Umbrella Rank: 883 10yr old
39 KB
2 googletagmanager.com
www.googletagmanager.com — Cisco Umbrella Rank: 44 14yr old
353 KB
1 yahoo.com
sp.analytics.yahoo.com — Cisco Umbrella Rank: 2654 13yr old
677 B
1 ggpht.com
yt3.ggpht.com — Cisco Umbrella Rank: 364 10yr old
2 KB
1 ytimg.com
i.ytimg.com — Cisco Umbrella Rank: 124 10yr old
55 KB
1 facebook.com
www.facebook.com — Cisco Umbrella Rank: 132 11yr old
20 B
1 educationliberia.org 1 redirects
www.educationliberia.org 24d old
294 B
109 19
Domain Requested by
42 www.givedirectly.org 2 redirects www.givedirectly.org
ajax.googleapis.com
15 www.youtube.com www.givedirectly.org
www.youtube.com
www.googletagmanager.com
7 erinaceus.givedirectly.org www.givedirectly.org
erinaceus.givedirectly.org
5 www.google.com www.googletagmanager.com
www.youtube.com
www.givedirectly.org
4 px.ads.linkedin.com 2 redirects www.givedirectly.org
snap.licdn.com
4 use.typekit.net www.givedirectly.org
use.typekit.net
3 googleads.g.doubleclick.net 1 redirects www.googletagmanager.com
www.youtube.com
3 fonts.gstatic.com fonts.googleapis.com
www.youtube.com
3 js.stripe.com www.givedirectly.org
js.stripe.com
2 m.stripe.network js.stripe.com
m.stripe.network
2 jnn-pa.googleapis.com www.youtube.com
2 analytics.google.com www.googletagmanager.com
2 s.yimg.com www.givedirectly.org
s.yimg.com
2 connect.facebook.net www.givedirectly.org
connect.facebook.net
2 snap.licdn.com www.googletagmanager.com
snap.licdn.com
2 www.googletagmanager.com www.givedirectly.org
www.googletagmanager.com
1 m.stripe.com m.stripe.network
1 sp.analytics.yahoo.com www.givedirectly.org
1 www.gstatic.com www.youtube.com
1 yt3.ggpht.com www.youtube.com
1 www.linkedin.com 1 redirects
1 i.ytimg.com www.youtube.com
1 www.facebook.com www.givedirectly.org
1 static.doubleclick.net www.youtube.com
1 stats.g.doubleclick.net www.googletagmanager.com
1 ad.doubleclick.net www.googletagmanager.com
1 donate.givedirectly.org www.givedirectly.org
1 p.typekit.net use.typekit.net
1 ajax.googleapis.com www.givedirectly.org
1 fonts.googleapis.com www.givedirectly.org
1 www.educationliberia.org 1 redirects
109 31
Subject Issuer Validity Valid
wordpress.givedirectly.org
Amazon RSA 2048 M04
2026-08-24 -
2027-03-09
7mo crt.sh
use.typekit.net
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2026-05-29 -
2026-12-13
7mo crt.sh
upload.video.google.com
WR2
2026-08-10 -
2026-11-02
3mo crt.sh
a.stripecdn.com
DigiCert EV RSA CA G2
2026-08-05 -
2026-11-12
3mo crt.sh
*.google-analytics.com
WR2
2026-08-10 -
2026-11-02
3mo crt.sh
*.givedirectly.org
Amazon RSA 2048 M01
2025-10-21 -
2026-11-18
1yr crt.sh
*.google.com
WE2
2026-08-10 -
2026-11-02
3mo crt.sh
*.gstatic.com
WR2
2026-08-10 -
2026-11-02
3mo crt.sh
laravel.givedirectly.org
Amazon RSA 2048 M04
2026-07-14 -
2027-01-27
7mo crt.sh
*.licdn.com
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2026-09-08 -
2027-03-25
7mo crt.sh
*.facebook.com
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2026-06-21 -
2026-09-19
3mo crt.sh
*.www.yahoo.com
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2026-08-17 -
2026-10-07
2mo crt.sh
*.doubleclick.net
WR2
2026-08-10 -
2026-11-02
3mo crt.sh
*.g.doubleclick.net
WR2
2026-08-10 -
2026-11-02
3mo crt.sh
edgestatic.com
WR2
2026-08-10 -
2026-11-02
3mo crt.sh
*.googleusercontent.com
WR2
2026-08-10 -
2026-11-02
3mo crt.sh
*.sp.analytics.yahoo.com
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2026-07-29 -
2026-10-21
3mo crt.sh
www.linkedin.com
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2026-04-16 -
2026-10-16
6mo crt.sh
m.stripe.com
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2026-07-28 -
2026-11-12
4mo crt.sh

This page contains 4 frames:

Primary Page: https://www.givedirectly.org/liberia
Frame ID: 55692C560A755B065936D8A7979F901E
Requests: 86 HTTP requests in this frame

Frame: https://www.youtube.com/embed/mCsv_yLgi3c?start=1&feature=oembed&enablejsapi=1&origin=https%3A%2F%2Fwww.givedirectly.org
Frame ID: 0D77EF2960BA9EB518D1444C4F99D5E6
Requests: 23 HTTP requests in this frame

Frame: https://js.stripe.com/v3/m-outer-3437aaddcdf6922d623e172c2d6f9278.html
Frame ID: F397CF07284075F2E9136FB4EE5B3AB1
Requests: 2 HTTP requests in this frame

Frame: https://m.stripe.network/inner.html
Frame ID: CFE1EE9D50E081B8AF3ED32E0887F91A
Requests: 3 HTTP requests in this frame

Screenshot

Page Title

Cash Aid in Liberia | GiveDirectly

Page URL History Show full URLs

  1. http://www.educationliberia.org/ HTTP 307
    https://www.educationliberia.org/ HTTP 307
    http://www.educationliberia.org/ HTTP 301
    https://www.givedirectly.org/education-stipends/ HTTP 301
    https://www.givedirectly.org/liberia/ HTTP 301
    https://www.givedirectly.org/liberia Page URL

Detected technologies

(CMS)
Overall confidence: 100%
Detected patterns
  • <link rel=["']stylesheet["'] [^>]+/wp-(?:content|includes)/
  • /wp-(?:content|includes)/

(Video players)
Overall confidence: 100%
Detected patterns
  • \.youtube\.com/

(Payment processors)
Overall confidence: 100%
Detected patterns
  • js\.stripe\.com

(Font scripts)
Overall confidence: 100%
Detected patterns
  • <link [^>]*href="[^"]+use\.typekit\.(?:net|com)

(Security)
Overall confidence: 100%
Detected patterns

(Advertising)
Overall confidence: 100%
Detected patterns
  • \.doubleclick\.net

(Analytics)
Overall confidence: 100%
Detected patterns
  • connect\.facebook\.\w+/.+/fbevents\.js
  • connect\.facebook.\w+/signals/config/\d+\?v=([\d\.]+)

(Analytics)
Overall confidence: 100%
Detected patterns
  • googletagmanager\.com/gtag/js

(CDN)
Overall confidence: 100%
Detected patterns
  • ajax\.googleapis\.com/ajax/libs/

(Tag managers)
Overall confidence: 100%
Detected patterns
  • googletagmanager\.com/gtm\.js
  • \.googletagmanager\.com/

(JavaScript libraries)
Overall confidence: 100%
Detected patterns
  • jquery
  • /(\d+\.\d+\.\d+)/jquery(?!\.popupoverlay\.js|(?:\.[\w-]*)*fancybox)[/.-][^u]

(Analytics)
Overall confidence: 100%
Detected patterns
  • snap\.licdn\.com/li\.lms-analytics/insight\.min\.js

(JavaScript libraries)
Overall confidence: 100%
Detected patterns
  • (?:/([\d.]+))?/slick(?:\.min)?\.js

(Font scripts)
Overall confidence: 100%
Detected patterns
  • <link [^>]*href="[^"]+use\.typekit\.(?:net|com)

Page Statistics

109
Requests

97 %
HTTPS

0 %
IPv6

19
Domains

31
Subdomains

33
IPs

2
Countries

5321 kB
Transfer

14626 kB
Size

28
Cookies

Page URL History

This captures the URL locations of the websites, including HTTP redirects and client-side redirects via JavaScript or Meta fields.

  1. http://www.educationliberia.org/ HTTP 307
    https://www.educationliberia.org/ HTTP 307
    http://www.educationliberia.org/ HTTP 301
    https://www.givedirectly.org/education-stipends/ HTTP 301
    https://www.givedirectly.org/liberia/ HTTP 301
    https://www.givedirectly.org/liberia Page URL

Redirected requests

There were HTTP redirect chains for the following requests:

Request Chain 88
  • https://googleads.g.doubleclick.net/pagead/id HTTP 302
  • https://googleads.g.doubleclick.net/pagead/id?slf_rd=1
Request Chain 98
  • https://px.ads.linkedin.com/collect?v=2&fmt=js&pid=5456490&time=1789216338378&li_adsId=09d7f9f8-2b51-43e4-a029-8a71ed0e2e49&url=https%3A%2F%2Fwww.givedirectly.org%2Fliberia HTTP 302
  • https://px.ads.linkedin.com/collect?v=2&fmt=js&pid=5456490&time=1789216338378&li_adsId=09d7f9f8-2b51-43e4-a029-8a71ed0e2e49&url=https%3A%2F%2Fwww.givedirectly.org%2Fliberia&cookiesTest=true HTTP 302
  • https://www.linkedin.com/px/li_sync?redirect=https%3A%2F%2Fpx.ads.linkedin.com%2Fcollect%3Fv%3D2%26fmt%3Djs%26pid%3D5456490%26time%3D1789216338378%26li_adsId%3D09d7f9f8-2b51-43e4-a029-8a71ed0e2e49%26url%3Dhttps%253A%252F%252Fwww.givedirectly.org%252Fliberia%26cookiesTest%3Dtrue%26liSync%3Dtrue HTTP 302
  • https://px.ads.linkedin.com/collect?v=2&fmt=js&pid=5456490&time=1789216338378&li_adsId=09d7f9f8-2b51-43e4-a029-8a71ed0e2e49&url=https%3A%2F%2Fwww.givedirectly.org%2Fliberia&cookiesTest=true&liSync=true

109 HTTP transactions
6 data transactions

Method
Protocol
Status Resource
Path
Size
x-fer
Time
Latency
Type
MIME-Type
IP
Location
GET
H3
200
Primary Request liberia Show response
www.givedirectly.org/
Redirect Chain
  • http://www.educationliberia.org/
  • https://www.educationliberia.org/
  • http://www.educationliberia.org/
  • https://www.givedirectly.org/education-stipends/
  • https://www.givedirectly.org/liberia/
  • https://www.givedirectly.org/liberia
284 KB
67 KB
506ms
506ms
Document
text/html
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) / PHP/8.5.9
Resource Hash
9743811b64846226fe68de5850229c713828eb05de3d9d6172462b64b07a63b7
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36

Response headers

alt-svc
h3=":443"; ma=86400
cache-control
public, max-age=60, stale-while-revalidate=300
content-encoding
gzip
content-type
text/html; charset=UTF-8
date
Sat, 12 Sep 2026 12:32:15 GMT
link
<https://www.givedirectly.org/wp-json/>; rel="https://api.w.org/" <https://www.givedirectly.org/wp-json/wp/v2/pages/13231>; rel="alternate"; title="JSON"; type="application/json" <https://www.givedirectly.org/?p=13231>; rel=shortlink
server
Apache/2.4.68 (Debian)
server-timing
wp-before-template;dur=113.77
strict-transport-security
max-age=31536000
vary
Accept-Encoding
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
x-amz-cf-id
hNpcUIhmJkrjMs37F-wlZFPycG-4XsxTNq4SNL6lBjzfga7d4ARINw==
x-amz-cf-pop
IAD61-P11
x-cache
Miss from cloudfront
x-frame-options
DENY
x-powered-by
PHP/8.5.9

Redirect headers

alt-svc
h3=":443"; ma=86400
cache-control
public, max-age=60, stale-while-revalidate=300
content-length
0
content-type
text/html; charset=UTF-8
date
Sat, 12 Sep 2026 12:32:14 GMT
expires
Wed, 11 Jan 1984 05:00:00 GMT
location
https://www.givedirectly.org/liberia
server
Apache/2.4.68 (Debian)
strict-transport-security
max-age=31536000
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
x-amz-cf-id
gnsfkeCaGrB7GNjybR_VkLEl9L8y0OkJQRPeY3mNyVL3PLnwuInOQw==
x-amz-cf-pop
IAD61-P11
x-cache
Miss from cloudfront
x-frame-options
DENY
x-powered-by
PHP/8.5.9
x-redirect-by
WordPress
GET
H3
200
style-blocks.build.css
www.givedirectly.org/wp-content/plugins/genesis-blocks/dist/
40 KB
6 KB
249ms
248ms
Stylesheet
text/css
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/plugins/genesis-blocks/dist/style-blocks.build.css?ver=1780909731
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
9b3a1ff454f7410838e773a7640b9bccc0bae845f4c4fe5daf03c11d60a9613b
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
alt-svc
h3=":443"; ma=86400
x-cache
Miss from cloudfront
x-amz-cf-id
1wBfmbrVF_m4FteZjGFalXc5NcAq5Iy78DlsPI3vICpR9AU88j9Q5A==
date
Sat, 12 Sep 2026 12:32:15 GMT
content-type
text/css
vary
Accept-Encoding
last-modified
Mon, 08 Jun 2026 09:08:51 GMT
x-frame-options
DENY
strict-transport-security
max-age=31536000
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
content-length
6238
x-amz-cf-pop
IAD61-P11
server
Apache/2.4.68 (Debian)
GET
H3
200
style.min.css
www.givedirectly.org/wp-includes/blocks/cover/
20 KB
2 KB
205ms
204ms
Stylesheet
text/css
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-includes/blocks/cover/style.min.css?ver=7.0.4
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
bd56a479237f7212eae3a46a3f0e9aeba7dff44dab300249a18fa24587fb63d0
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
alt-svc
h3=":443"; ma=86400
x-cache
Miss from cloudfront
x-amz-cf-id
-LDltuLff37eth_s4k21BM41yEpLg2ILliC3EncN4kt4BB-w3LnomQ==
date
Sat, 12 Sep 2026 12:32:15 GMT
content-type
text/css
vary
Accept-Encoding
last-modified
Tue, 06 Jan 2026 10:50:06 GMT
x-frame-options
DENY
strict-transport-security
max-age=31536000
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
content-length
1846
x-amz-cf-pop
IAD61-P11
server
Apache/2.4.68 (Debian)
GET
H2
200
nwb0fwu.css
use.typekit.net/
3 KB
985 B
548ms
220ms
Stylesheet
text/css
23.215.0.145
AKAMAI-ASN1 Akama...
General
Full URL
https://use.typekit.net/nwb0fwu.css
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
23.215.0.145 Ashburn, United States, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a23-215-0-145.deploy.static.akamaitechnologies.com
Software
nginx /
Resource Hash
7e7a3bbb1955e053b838b91c6659278d2c987a068aed0b9e93a438a071f84709
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains;

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains;
cache-control
private, max-age=600, stale-while-revalidate=604800
timing-allow-origin
*
content-encoding
gzip
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
content-length
729
date
Sat, 12 Sep 2026 12:32:15 GMT
akamai-grn
0.91f6d517.1789216335.5c75df2e
content-type
text/css;charset=utf-8
vary
Accept-Encoding
server
nginx
GET
H2
200
css2
fonts.googleapis.com/
4 KB
1 KB
504ms
200ms
Stylesheet
text/css
142.251.163.95
Google LLC
General
Full URL
https://fonts.googleapis.com/css2?family=Inter:ital,opsz,wght@0,14..32,100..900;1,14..32,100..900
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
142.251.163.95 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
wv-in-f95.1e100.net
Software
ESF /
Resource Hash
de5e3ac842421180e0fd836bdaf1e1f93216d501fc5800b429797f53956d1d35
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-content-type-options
nosniff
expires
Sat, 12 Sep 2026 12:32:15 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sat, 12 Sep 2026 12:32:15 GMT
content-type
text/css; charset=utf-8
vary
Sec-Fetch-Dest, Sec-Fetch-Mode, Sec-Fetch-Site
last-modified
Sat, 12 Sep 2026 12:24:06 GMT
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=31536000
link
<https://fonts.gstatic.com>; rel=preconnect; crossorigin
cache-control
private, max-age=86400, stale-while-revalidate=604800
timing-allow-origin
*
cross-origin-opener-policy
same-origin-allow-popups
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
x-xss-protection
0
server
ESF
GET
H3
200
styles.min.css
www.givedirectly.org/wp-content/themes/givedirectly/css/
274 KB
42 KB
261ms
261ms
Stylesheet
text/css
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/themes/givedirectly/css/styles.min.css?ver=1787903358
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
c56bfcd8aa023d34a83bb9bbac9cd2325cf6bef3f357f0bd86a33dbcc905027e
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
alt-svc
h3=":443"; ma=86400
x-cache
Miss from cloudfront
x-amz-cf-id
vo9WBGyUGDJYpjj71w2UNXw2k_lWyiaoz8vi3VhA2lh8gAZ_Lk4NbQ==
date
Sat, 12 Sep 2026 12:32:15 GMT
content-type
text/css
vary
Accept-Encoding
last-modified
Fri, 28 Aug 2026 07:49:18 GMT
x-frame-options
DENY
strict-transport-security
max-age=31536000
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
content-length
42374
x-amz-cf-pop
IAD61-P11
server
Apache/2.4.68 (Debian)
GET
H3
200
/ Show response
js.stripe.com/v3/
1 MB
253 KB
248ms
125ms
Script
text/javascript
3.171.38.13
Amazon.com
General
Full URL
https://js.stripe.com/v3/
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
3.171.38.13 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-171-38-13.iad61.r.cloudfront.net
Software
Cloudfront /
Resource Hash
ad1ee1351e9e831c255405b95cef5279f74119e03464a23093e59f513e6f2aa0
Security Headers
Name Value
Strict-Transport-Security max-age=31556926; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
etag
W/"3675b802a0153b7d4be5dacae75556c7"
age
82
x-content-type-options
nosniff
alt-svc
h3=":443"; ma=86400
x-cache
Hit from cloudfront
x-amz-cf-id
6qiidXoPM_X3oSP57pTuxHMNdq9ZFoc0cOJ6Ox2tQ5tQp3CPnNTsXA==
date
Sat, 12 Sep 2026 12:31:45 GMT
content-type
text/javascript; charset=utf-8
last-modified
Fri, 11 Sep 2026 21:17:09 GMT
vary
Accept-Encoding
strict-transport-security
max-age=31556926; includeSubDomains; preload
cache-control
max-age=120
timing-allow-origin
*
via
1.1 ed55c0a01ce6fa50a84c10d7312476d0.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-amz-cf-pop
IAD61-P7
server
Cloudfront
GET
H3
200
Liberia-background-flip.png
www.givedirectly.org/wp-content/uploads/2024/03/
1 MB
1 MB
267ms
267ms
Image
image/png
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/uploads/2024/03/Liberia-background-flip.png
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
6aa8b7c94c8dd93a37474c0fe40fcde67fcac48cf0faebc6d8f96c8d843ccd88
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
vary
Accept-Encoding
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
alt-svc
h3=":443"; ma=86400
x-cache
RefreshHit from cloudfront
content-length
1168283
x-amz-cf-id
p76dZhgx0ux9fiuE9sbfyaUBU1Zm1wCS3LsgynCeRImY-d_b_vyEFg==
date
Sat, 12 Sep 2026 12:32:15 GMT
content-type
image/png
last-modified
Mon, 07 Apr 2025 18:14:42 GMT
server
Apache/2.4.68 (Debian)
x-amz-cf-pop
IAD61-P11
x-frame-options
DENY
GET
H3
200
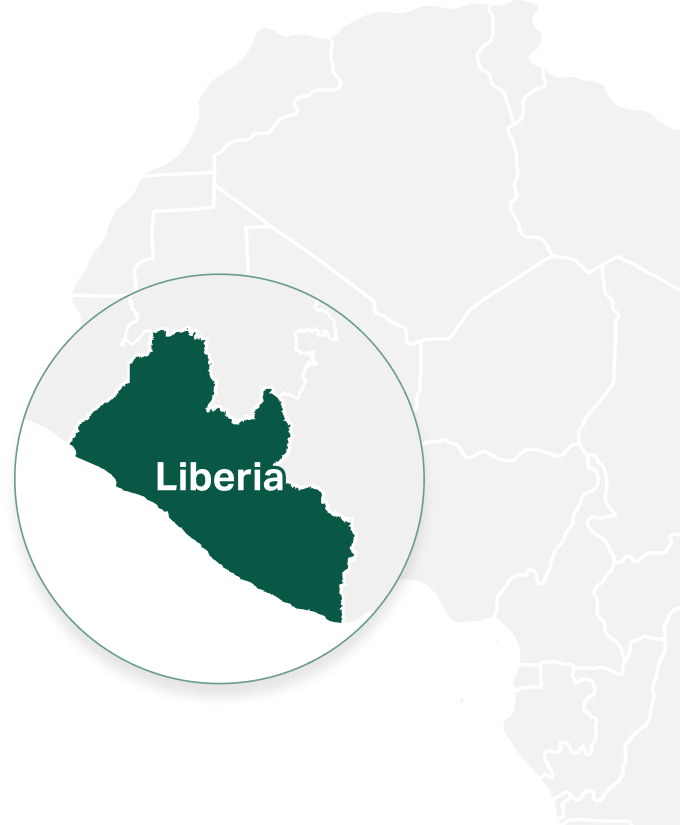
Africa-map-highlighting-Liberia.png
www.givedirectly.org/wp-content/uploads/2024/04/
34 KB
34 KB
272ms
271ms
Image
image/png
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/uploads/2024/04/Africa-map-highlighting-Liberia.png
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
9cbea185b2208b219f0b0137ff09375b5ea40735b46e36587ec1aaef44875a95
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
vary
Accept-Encoding
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
alt-svc
h3=":443"; ma=86400
x-cache
RefreshHit from cloudfront
content-length
34644
x-amz-cf-id
ieopYd0yIOaDatCtb2HpywelAIFEgEm5PrLe6SkHYpMBA05zbQbYKg==
date
Sat, 12 Sep 2026 12:32:15 GMT
content-type
image/png
last-modified
Mon, 07 Apr 2025 18:24:06 GMT
server
Apache/2.4.68 (Debian)
x-amz-cf-pop
IAD61-P11
x-frame-options
DENY
GET
H3
200
USAID-logo-20230517.svg
www.givedirectly.org/wp-content/uploads/2023/05/
353 KB
114 KB
269ms
268ms
Image
image/svg+xml
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/uploads/2023/05/USAID-logo-20230517.svg
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
f8a26c88ffc70bb0b322ae2df632fbbaaafeec0702b2e808fd8b5358fd8880a8
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
vary
Accept-Encoding
cache-control
public, max-age=60, stale-while-revalidate=300
content-encoding
br
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
alt-svc
h3=":443"; ma=86400
x-cache
RefreshHit from cloudfront
x-amz-cf-id
Avdc_diZqBm1FQFyfyf6j1L8v9kZHYMYmzFAZWldxEJ-UdGBsg_fOw==
date
Sat, 12 Sep 2026 12:32:15 GMT
content-type
image/svg+xml
x-amz-cf-pop
IAD61-P11
server
Apache/2.4.68 (Debian)
last-modified
Mon, 07 Apr 2025 17:16:31 GMT
x-frame-options
DENY
GET
H3
200
Basic-income-video-cover-1.png
www.givedirectly.org/wp-content/uploads/2024/03/
1000 KB
1001 KB
200ms
199ms
Image
image/png
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/uploads/2024/03/Basic-income-video-cover-1.png
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
529b5b205dcd5ab2c9e1d1308fee462193f4d8b3524e36ba58d0609868ffb31c
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
vary
Accept-Encoding
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
alt-svc
h3=":443"; ma=86400
x-cache
RefreshHit from cloudfront
content-length
1024421
x-amz-cf-id
gVjumnRLUf1o6I98CWutjd3m3cgWWUOGuX0nL0-WR3BuMs0oPhzxyg==
date
Sat, 12 Sep 2026 12:32:15 GMT
content-type
image/png
last-modified
Mon, 07 Apr 2025 18:19:31 GMT
server
Apache/2.4.68 (Debian)
x-amz-cf-pop
IAD61-P11
x-frame-options
DENY
GET
H2
200
jquery.min.js Show response
ajax.googleapis.com/ajax/libs/jquery/3.7.0/
85 KB
30 KB
518ms
185ms
Script
text/javascript
192.178.155.95
Google LLC
General
Full URL
https://ajax.googleapis.com/ajax/libs/jquery/3.7.0/jquery.min.js?ver=1787903358
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
192.178.155.95 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
yuiadrs-in-f95.1e100.net
Software
sffe /
Resource Hash
d8f9afbf492e4c139e9d2bcb9ba6ef7c14921eb509fb703bc7a3f911b774eff8
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
report-to
{"group":"hosted-libraries-pushers","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/hosted-libraries-pushers"}]}
x-content-type-options
nosniff
expires
Sun, 12 Sep 2027 12:32:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sat, 12 Sep 2026 12:32:16 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
last-modified
Wed, 17 May 2023 18:15:00 GMT
cache-control
public, max-age=31536000, stale-while-revalidate=2592000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="hosted-libraries-pushers"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/hosted-libraries-pushers
accept-ranges
bytes
access-control-allow-origin
*
content-length
30433
x-xss-protection
0
server
sffe
GET
H3
200
slick.js Show response
www.givedirectly.org/wp-content/themes/givedirectly/js/
87 KB
15 KB
266ms
265ms
Script
text/javascript
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/themes/givedirectly/js/slick.js
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
9baa573e4378873b7ac81ccb1d954ce9bb2b1a933947ad3012263ddc604d8505
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
alt-svc
h3=":443"; ma=86400
x-cache
Miss from cloudfront
x-amz-cf-id
JHAwE03JG_kFRffxdxn9x1xOlTS7tNtLNipxJHxKv7iOFQyHng8KJA==
date
Sat, 12 Sep 2026 12:32:16 GMT
content-type
text/javascript
vary
Accept-Encoding
last-modified
Fri, 28 Aug 2026 07:48:46 GMT
x-frame-options
DENY
strict-transport-security
max-age=31536000
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
content-length
15071
x-amz-cf-pop
IAD61-P11
server
Apache/2.4.68 (Debian)
GET
H3
200
footer-scripts.min.js Show response
www.givedirectly.org/wp-content/themes/givedirectly/js/
80 KB
22 KB
202ms
201ms
Script
text/javascript
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/themes/givedirectly/js/footer-scripts.min.js?ver=1787903358
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
27b14e9c51de61009538b1b24a725ae1105f6893df957f8da3003ab6ab076cd4
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
alt-svc
h3=":443"; ma=86400
x-cache
Miss from cloudfront
x-amz-cf-id
03ipTP1qE4CTfVU9ruZH7TvXhUkYIfbeAJLqU9e1v87tko4jV0Yevg==
date
Sat, 12 Sep 2026 12:32:16 GMT
content-type
text/javascript
vary
Accept-Encoding
last-modified
Fri, 28 Aug 2026 07:49:19 GMT
x-frame-options
DENY
strict-transport-security
max-age=31536000
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
content-length
22693
x-amz-cf-pop
IAD61-P11
server
Apache/2.4.68 (Debian)
GET
H3
200
script.js Show response
www.givedirectly.org/wp-content/themes/givedirectly/blocks/gd-show-more/wrapper/
353 B
528 B
133ms
132ms
Script
text/javascript
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/themes/givedirectly/blocks/gd-show-more/wrapper/script.js?ver=0.1
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
0f0024b428a219528079eb53d4a21f8e1b8893d0bec5bdfadb24e7fffb3954ec
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
age
212
alt-svc
h3=":443"; ma=86400
x-cache
Hit from cloudfront
x-amz-cf-id
uBFurdV9w3UAelAwom0r4nNtqjhTPsyL5JWwlHQoTCoM3AJYygqYzA==
date
Sat, 12 Sep 2026 12:28:44 GMT
content-type
text/javascript
vary
Accept-Encoding
last-modified
Fri, 28 Aug 2026 07:48:46 GMT
x-frame-options
DENY
strict-transport-security
max-age=31536000
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
content-length
202
x-amz-cf-pop
IAD61-P11
server
Apache/2.4.68 (Debian)
GET
H2
200
p.css
p.typekit.net/
5 B
172 B
788ms
240ms
Stylesheet
text/css
23.215.0.138
AKAMAI-ASN1 Akama...
General
Full URL
https://p.typekit.net/p.css?s=1&k=nwb0fwu&ht=tk&f=14032.14033.14034.14038&a=35674917&app=typekit&e=css
Requested by
Host: use.typekit.net
URL: https://use.typekit.net/nwb0fwu.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
23.215.0.138 Ashburn, United States, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a23-215-0-138.deploy.static.akamaitechnologies.com
Software
nginx /
Resource Hash
1c0ff118a4290c99f39c90abb38703a866e47251b23cca20266c69c812ccafeb

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://use.typekit.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
public, max-age=604800
etag
"6a7bc0a2-5"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
content-length
5
date
Sat, 12 Sep 2026 12:32:16 GMT
content-type
text/css
last-modified
Wed, 12 Aug 2026 00:38:58 GMT
server
nginx
GET
H2
200
gtm.js Show response
www.googletagmanager.com/
513 KB
169 KB
602ms
230ms
Script
application/javascript
142.251.179.97
Google LLC
General
Full URL
https://www.googletagmanager.com/gtm.js?id=GTM-PJNMMGH
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.179.97 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pd-in-f97.1e100.net
Software
Google Tag Manager /
Resource Hash
97a50332c2d8403e8bb2a89c563a0ab9c66cd5bb77a855aebd6c6b13864b54a3
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
zstd
expires
Sat, 12 Sep 2026 12:32:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sat, 12 Sep 2026 12:32:17 GMT
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
last-modified
Sat, 12 Sep 2026 12:00:00 GMT
access-control-allow-headers
Cache-Control
strict-transport-security
max-age=31536000; includeSubDomains
cache-control
private, max-age=900
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
access-control-allow-origin
*
content-length
172580
x-xss-protection
0
server
Google Tag Manager
GET
H3
200
array.js Show response
erinaceus.givedirectly.org/static/
298 KB
93 KB
299ms
139ms
Script
application/javascript
3.167.69.84
Amazon.com
General
Full URL
https://erinaceus.givedirectly.org/static/array.js
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
3.167.69.84 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-167-69-84.iad61.r.cloudfront.net
Software
cloudflare /
Resource Hash
67a7d9f64d1fd0d1000a3ad434cdead195b8394f17d47ec936087450febc5d3b
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 1; mode=block

Request headers

Origin
https://www.givedirectly.org
sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
3000
access-control-expose-headers
ETag
content-encoding
gzip
cf-cache-status
REVALIDATED
x-amz-version-id
95cLj2DUfdZ1SA8jpaGYzUM08JH7fU8n
etag
W/"e0fae82b991765db52fc5400a16a242c"
age
3659
access-control-allow-methods
POST, GET, DELETE, PUT
x-content-type-options
nosniff
x-cache
Hit from cloudfront
x-amz-cf-id
J--OhJtqmrtv7MtKoREFerXKJVTOXqNCZmduEMbOcJIhV6KPhKDzeg==
date
Sat, 12 Sep 2026 11:32:23 GMT
content-type
application/javascript
last-modified
Fri, 11 Sep 2026 09:21:48 GMT
vary
Origin,Accept-Encoding
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=31536000
cache-control
public, max-age=14400
referrer-policy
strict-origin-when-cross-origin
via
1.1 cf8c5b66c93d44ff2109ede7dd215622.cloudfront.net (CloudFront)
cf-ray
a39bd3ffaa5dc9a3-IAD
access-control-allow-origin
*
x-xss-protection
1; mode=block
x-amz-cf-pop
IAD61-P6
server
cloudflare
x-amz-server-side-encryption
AES256
GET
H2
200
mCsv_yLgi3c Show response
www.youtube.com/embed/ Frame 0D77
149 KB
62 KB
529ms
166ms
Document
text/html
142.251.153.4
Google LLC
General
Full URL
https://www.youtube.com/embed/mCsv_yLgi3c?start=1&feature=oembed
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.153.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
d68b224c0e01b62d9384bdf1a607c3c128b67b632ae093efc8a393d8592de242
Security Headers
Name Value
Content-Security-Policy script-src 'unsafe-eval' 'self' 'unsafe-inline' https://www.google.com https://apis.google.com https://ssl.gstatic.com https://www.gstatic.com https://www.googletagmanager.com https://www.google-analytics.com https://*.youtube.com https://*.google.com https://*.gstatic.com https://youtube.com https://www.youtube.com https://google.com https://*.doubleclick.net https://*.googleapis.com https://www.googleadservices.com https://tpc.googlesyndication.com https://www.youtubekids.com https://www.youtube-nocookie.com https://www.youtubeeducation.com https://www-onepick-opensocial.googleusercontent.com;report-uri https://csp.withgoogle.com/csp/youtube_main/allowlist base-uri 'self';object-src 'none';script-src 'report-sample' 'nonce-KFSxrVZSMgW9FKIGo283RQ' 'unsafe-inline' 'strict-dynamic' https: http: 'unsafe-eval';report-uri https://csp.withgoogle.com/csp/youtube_main/strict require-trusted-types-for 'script'
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://www.givedirectly.org/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cache-control
no-cache, no-store, max-age=0, must-revalidate
content-encoding
br
content-security-policy
script-src 'unsafe-eval' 'self' 'unsafe-inline' https://www.google.com https://apis.google.com https://ssl.gstatic.com https://www.gstatic.com https://www.googletagmanager.com https://www.google-analytics.com https://*.youtube.com https://*.google.com https://*.gstatic.com https://youtube.com https://www.youtube.com https://google.com https://*.doubleclick.net https://*.googleapis.com https://www.googleadservices.com https://tpc.googlesyndication.com https://www.youtubekids.com https://www.youtube-nocookie.com https://www.youtubeeducation.com https://www-onepick-opensocial.googleusercontent.com;report-uri https://csp.withgoogle.com/csp/youtube_main/allowlist base-uri 'self';object-src 'none';script-src 'report-sample' 'nonce-KFSxrVZSMgW9FKIGo283RQ' 'unsafe-inline' 'strict-dynamic' https: http: 'unsafe-eval';report-uri https://csp.withgoogle.com/csp/youtube_main/strict require-trusted-types-for 'script'
content-type
text/html; charset=utf-8
cross-origin-embedder-policy-report-only
require-corp; report-to="youtube_main"
cross-origin-opener-policy-report-only
same-origin; report-to="youtube_main"
cross-origin-resource-policy
cross-origin
date
Sat, 12 Sep 2026 12:32:17 GMT
expires
Mon, 01 Jan 1990 00:00:00 GMT
origin-trial
AmhMBR6zCLzDDxpW+HfpP67BqwIknWnyMOXOQGfzYswFmJe+fgaI6XZgAzcxOrzNtP7hEDsOo1jdjFnVr2IdxQ4AAAB4eyJvcmlnaW4iOiJodHRwczovL3lvdXR1YmUuY29tOjQ0MyIsImZlYXR1cmUiOiJXZWJWaWV3WFJlcXVlc3RlZFdpdGhEZXByZWNhdGlvbiIsImV4cGlyeSI6MTc1ODA2NzE5OSwiaXNTdWJkb21haW4iOnRydWV9 AiDEBptUfVeO93q48VdVMe/ubupazdAl8AaHP+NBzdnW8quUcHdzJUyGSfrmtpKJu7EOvwRp9ug2rEo3XU+WMAMAAAB2eyJvcmlnaW4iOiJodHRwczovL3lvdXR1YmUuY29tOjQ0MyIsImZlYXR1cmUiOiJEZXZpY2VCb3VuZFNlc3Npb25DcmVkZW50aWFsczIiLCJleHBpcnkiOjE3NzQzMTA0MDAsImlzU3ViZG9tYWluIjp0cnVlfQ==
p3p
CP="This is not a P3P policy! See http://support.google.com/accounts/answer/151657?hl=en for more info."
permissions-policy
ch-ua-arch=*, ch-ua-bitness=*, ch-ua-full-version=*, ch-ua-full-version-list=*, ch-ua-model=*, ch-ua-wow64=*, ch-ua-form-factors=*, ch-ua-platform=*, ch-ua-platform-version=*
pragma
no-cache
report-to
{"group":"youtube_main","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube_main"}]}
server
ESF
strict-transport-security
max-age=31536000
vary
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
x-content-type-options
nosniff
x-xss-protection
0
GET
H3
206
Sending-money-to-the-one-of-the-poorest-places-in-the-world-_-GiveDirectly-in-Liberia.mp4
www.givedirectly.org/wp-content/uploads/2026/03/
480 KB
0
350ms
342ms
Media
video/mp4
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/uploads/2026/03/Sending-money-to-the-one-of-the-poorest-places-in-the-world-_-GiveDirectly-in-Liberia.mp4
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
Accept-Encoding
identity;q=1, *;q=0
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Range
bytes=0-
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
cache-control
public, max-age=60, stale-while-revalidate=300
Content-Range
bytes 0-60151586/60151587
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
alt-svc
h3=":443"; ma=86400
x-cache
Miss from cloudfront
Content-Length
60151587
x-amz-cf-id
hXC0KEHpNjIObd45fsC_JB5begS5yw_OoJXgkP3WmdApMm80ydwSIg==
date
Sat, 12 Sep 2026 12:32:16 GMT
content-type
video/mp4
last-modified
Sun, 29 Mar 2026 09:35:09 GMT
server
Apache/2.4.68 (Debian)
x-amz-cf-pop
IAD61-P11
x-frame-options
DENY
GET
DATA
200
OK
truncated
/
547 B
0
Image
image/svg+xml

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
eb14baeac955bb11e33cd7fd3fd2f698cf20db1b450325f45ea843b6cdc82366

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/svg+xml
GET
DATA
200
OK
truncated
/
552 B
0
Image
image/svg+xml

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
62f3f809487194fcc55a3ebd88811a604ae496027bb425d4ebd15d9ae1921945

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/svg+xml
GET
DATA
200
OK
truncated
/
380 B
0
Image
image/svg+xml

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
717f6bb5f6cc69c444f54376a72dee0ca7968b2a12e7c9475247ec85c0e75a53

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/svg+xml
GET
H3
200
white-pin.svg
www.givedirectly.org/wp-content/themes/givedirectly/img/icons/
2 KB
1 KB
202ms
202ms
Image
image/svg+xml
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/themes/givedirectly/img/icons/white-pin.svg
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/wp-content/themes/givedirectly/css/styles.min.css?ver=1787903358
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
7bd45ce8a39f954d4ca2c3da0c86ec3c772896313952e80abb669fe211c8a24f
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/wp-content/themes/givedirectly/css/styles.min.css?ver=1787903358
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
vary
Accept-Encoding
cache-control
public, max-age=60, stale-while-revalidate=300
content-encoding
br
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
alt-svc
h3=":443"; ma=86400
x-cache
Miss from cloudfront
x-amz-cf-id
JtDTQ6pM9eIEjUIVCjQi7hY2L-QBDDcYYyvHCUfnezJOCZb3cxDhNw==
date
Sat, 12 Sep 2026 12:32:16 GMT
content-type
image/svg+xml
x-amz-cf-pop
IAD61-P11
server
Apache/2.4.68 (Debian)
last-modified
Fri, 28 Aug 2026 07:48:46 GMT
x-frame-options
DENY
GET
H2
200
l
use.typekit.net/af/28158e/00000000000000003b9b4066/27/
27 KB
27 KB
477ms
215ms
Font
application/font-woff2
23.215.0.145
AKAMAI-ASN1 Akama...
General
Full URL
https://use.typekit.net/af/28158e/00000000000000003b9b4066/27/l?primer=7cdcb44be4a7db8877ffa5c0007b8dd865b3bbc383831fe2ea177f62257a9191&fvd=n4&v=3
Requested by
Host: use.typekit.net
URL: https://use.typekit.net/nwb0fwu.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
23.215.0.145 Ashburn, United States, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a23-215-0-145.deploy.static.akamaitechnologies.com
Software
nginx /
Resource Hash
09d305a5a1c4756015b5b0c509dcc3f121a6e9a754a92ed5bacbb5a60899d411

Request headers

Origin
https://www.givedirectly.org
sec-ch-ua-platform
"Linux"
Referer
https://use.typekit.net/nwb0fwu.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
public, max-age=31536000
timing-allow-origin
*
etag
"72f47cc4cd2aeefe0b7a3afe57823f9d1af1047c"
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
content-length
27196
date
Sat, 12 Sep 2026 12:32:16 GMT
akamai-grn
0.8ff6d517.1789216336.5c373e1f
content-type
application/font-woff2
server
nginx
GET
H3
200
UcCo3FwrK3iLTcviYwY.woff2
fonts.gstatic.com/s/inter/v20/
71 KB
71 KB
301ms
123ms
Font
font/woff2
142.250.31.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/inter/v20/UcCo3FwrK3iLTcviYwY.woff2
Requested by
Host: fonts.googleapis.com
URL: https://fonts.googleapis.com/css2?family=Inter:ital,opsz,wght@0,14..32,100..900;1,14..32,100..900
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.250.31.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bj-in-f94.1e100.net
Software
sffe /
Resource Hash
2c295d99e26dcf357d4d01bcf270fd6924b600c9a13dd8c363ef114f4c6976fa
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://www.givedirectly.org
sec-ch-ua-platform
"Linux"
Referer
https://fonts.googleapis.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

age
2263
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Sun, 12 Sep 2027 11:54:33 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sat, 12 Sep 2026 11:54:33 GMT
last-modified
Tue, 09 Sep 2025 18:33:17 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
72920
x-xss-protection
0
server
sffe
GET
H2
200
l
use.typekit.net/af/62681e/00000000000000003b9b406a/27/
29 KB
29 KB
531ms
270ms
Font
application/font-woff2
23.215.0.145
AKAMAI-ASN1 Akama...
General
Full URL
https://use.typekit.net/af/62681e/00000000000000003b9b406a/27/l?primer=7cdcb44be4a7db8877ffa5c0007b8dd865b3bbc383831fe2ea177f62257a9191&fvd=n7&v=3
Requested by
Host: use.typekit.net
URL: https://use.typekit.net/nwb0fwu.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
23.215.0.145 Ashburn, United States, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a23-215-0-145.deploy.static.akamaitechnologies.com
Software
nginx /
Resource Hash
d489b866f669f2f15392d5cdce4b6e23f9e66fd7e0f38155510282f5e68c8ec2

Request headers

Origin
https://www.givedirectly.org
sec-ch-ua-platform
"Linux"
Referer
https://use.typekit.net/nwb0fwu.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
public, max-age=31536000
timing-allow-origin
*
etag
"159fcd6e6aa88378b15160b2c3ced3c0d32dbe0c"
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
content-length
29384
date
Sat, 12 Sep 2026 12:32:16 GMT
akamai-grn
0.8ff6d517.1789216336.5c373e21
content-type
application/font-woff2
server
nginx
GET
H2
200
l
use.typekit.net/af/e604a2/00000000000000003b9b4069/27/
29 KB
29 KB
399ms
137ms
Font
application/font-woff2
23.215.0.145
AKAMAI-ASN1 Akama...
General
Full URL
https://use.typekit.net/af/e604a2/00000000000000003b9b4069/27/l?primer=7cdcb44be4a7db8877ffa5c0007b8dd865b3bbc383831fe2ea177f62257a9191&fvd=n5&v=3
Requested by
Host: use.typekit.net
URL: https://use.typekit.net/nwb0fwu.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
23.215.0.145 Ashburn, United States, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a23-215-0-145.deploy.static.akamaitechnologies.com
Software
nginx /
Resource Hash
b944b9469a2b4f007755ac5c43b4101d568cbcd2bda8f20f725ebb90e64674ea

Request headers

Origin
https://www.givedirectly.org
sec-ch-ua-platform
"Linux"
Referer
https://use.typekit.net/nwb0fwu.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
public, max-age=31536000
timing-allow-origin
*
etag
"d2aae8ad4fcc128b83ad3b0046449257b5817073"
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
content-length
29744
date
Sat, 12 Sep 2026 12:32:16 GMT
akamai-grn
0.8ff6d517.1789216336.5c373e23
content-type
application/font-woff2
server
nginx
GET
H3
200
Ministry-of-Education-Logo.png
www.givedirectly.org/wp-content/uploads/2024/03/
17 KB
17 KB
211ms
210ms
Image
image/png
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/uploads/2024/03/Ministry-of-Education-Logo.png
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
a29773a5a18b27354f0fc08df3705cb3606615e255f3321f791294cbe630c40e
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
vary
Accept-Encoding
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
alt-svc
h3=":443"; ma=86400
x-cache
RefreshHit from cloudfront
content-length
17051
x-amz-cf-id
2BE8p2K4ojkXqp0HW60Ikp5hg9QbxKtgCO9GRdgkfocLu6-N-rVQ5g==
date
Sat, 12 Sep 2026 12:32:16 GMT
content-type
image/png
last-modified
Mon, 07 Apr 2025 18:19:25 GMT
server
Apache/2.4.68 (Debian)
x-amz-cf-pop
IAD61-P11
x-frame-options
DENY
GET
H3
200
Liberia-Ministry-of-Gender-logo-150x150.png
www.givedirectly.org/wp-content/uploads/2024/03/
7 KB
8 KB
227ms
225ms
Image
image/png
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/uploads/2024/03/Liberia-Ministry-of-Gender-logo-150x150.png
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
b617a5a17c7568b46b5e2a514917282e709eef137fe4d673f31224bcc13fcdd0
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
vary
Accept-Encoding
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
alt-svc
h3=":443"; ma=86400
x-cache
RefreshHit from cloudfront
content-length
7638
x-amz-cf-id
--Bqcwp-jaGdVumsqUbbEGeDh8c8Cr3dWKaPEhXn5iZebEyB_2XOTA==
date
Sat, 12 Sep 2026 12:32:16 GMT
content-type
image/png
last-modified
Mon, 07 Apr 2025 18:17:27 GMT
server
Apache/2.4.68 (Debian)
x-amz-cf-pop
IAD61-P11
x-frame-options
DENY
GET
H3
200
National-Identificaiton-Registry-Logo.png
www.givedirectly.org/wp-content/uploads/2024/03/
24 KB
24 KB
205ms
200ms
Image
image/png
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/uploads/2024/03/National-Identificaiton-Registry-Logo.png
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
6cfea94a47e78a421a9bab12ab484dc77fb3ea83d340d43946d96fd0ab31219f
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
vary
Accept-Encoding
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
alt-svc
h3=":443"; ma=86400
x-cache
RefreshHit from cloudfront
content-length
24611
x-amz-cf-id
jIa58HII00hsY7eN082bYVvm7Dejps7FmfueehtMKlEjstwwvMTXLQ==
date
Sat, 12 Sep 2026 12:32:16 GMT
content-type
image/png
last-modified
Mon, 07 Apr 2025 18:19:24 GMT
server
Apache/2.4.68 (Debian)
x-amz-cf-pop
IAD61-P11
x-frame-options
DENY
GET
H3
200
King-Philanthropies-Logo-300x157.webp
www.givedirectly.org/wp-content/uploads/2024/03/
2 KB
3 KB
210ms
205ms
Image
image/webp
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/uploads/2024/03/King-Philanthropies-Logo-300x157.webp
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
7b17d6832b35cc032a658ba6b45c1538ce968b838d55d9919de6ffa976935a98
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
vary
Accept-Encoding
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
alt-svc
h3=":443"; ma=86400
x-cache
RefreshHit from cloudfront
content-length
2286
x-amz-cf-id
sDZpIhlB_AfAlZSv7Q14opxw0T2zX1UBopGtBQJApRMd03EciLxoLg==
date
Sat, 12 Sep 2026 12:32:16 GMT
content-type
image/webp
last-modified
Mon, 07 Apr 2025 18:17:29 GMT
server
Apache/2.4.68 (Debian)
x-amz-cf-pop
IAD61-P11
x-frame-options
DENY
GET
H3
200
Lonestarcell-MTN-logo.png
www.givedirectly.org/wp-content/uploads/2024/03/
2 KB
2 KB
202ms
197ms
Image
image/png
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/uploads/2024/03/Lonestarcell-MTN-logo.png
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
00c92e62c4c10775a27a8085d8646d8e439f900de55097bb1daac2ee87b2c887
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
vary
Accept-Encoding
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
alt-svc
h3=":443"; ma=86400
x-cache
RefreshHit from cloudfront
content-length
2154
x-amz-cf-id
fuiFbWebMxqH_qpiS9Q5Izl5Q3P4dE6L6F-8IWxTh7MoE4tsBPaX-Q==
date
Sat, 12 Sep 2026 12:32:16 GMT
content-type
image/png
last-modified
Mon, 07 Apr 2025 18:14:54 GMT
server
Apache/2.4.68 (Debian)
x-amz-cf-pop
IAD61-P11
x-frame-options
DENY
GET
H3
200
network-for-empowerment-progressive-initiatives-logo-300x164.png
www.givedirectly.org/wp-content/uploads/2024/03/
15 KB
16 KB
262ms
257ms
Image
image/png
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/uploads/2024/03/network-for-empowerment-progressive-initiatives-logo-300x164.png
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
2236b2368aeb6841735bbb7901ef75dca8ca81e24464aa0d9dcfec79d272e74d
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
vary
Accept-Encoding
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
alt-svc
h3=":443"; ma=86400
x-cache
RefreshHit from cloudfront
content-length
15692
x-amz-cf-id
Bvf3jhbvOYhzqk9LZwgrrZ_qpZgO5s5x5OkaZyduWb67DSf3bsXv6w==
date
Sat, 12 Sep 2026 12:32:16 GMT
content-type
image/png
last-modified
Mon, 07 Apr 2025 18:19:39 GMT
server
Apache/2.4.68 (Debian)
x-amz-cf-pop
IAD61-P11
x-frame-options
DENY
GET
H3
200
RTI-International-Logo-300x133.png
www.givedirectly.org/wp-content/uploads/2024/03/
7 KB
7 KB
259ms
254ms
Image
image/png
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/uploads/2024/03/RTI-International-Logo-300x133.png
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
0985d5b9720cf359347e5c471165fe3e9c1e069caa2e4bd213ac038c562c36ea
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
vary
Accept-Encoding
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
alt-svc
h3=":443"; ma=86400
x-cache
RefreshHit from cloudfront
content-length
7022
x-amz-cf-id
RTclrrU0F2oWCX1ePcUQlxoL4iaijRoRWtGA1VcnW-1UObcmqqu-Wg==
date
Sat, 12 Sep 2026 12:32:16 GMT
content-type
image/png
last-modified
Mon, 07 Apr 2025 18:16:06 GMT
server
Apache/2.4.68 (Debian)
x-amz-cf-pop
IAD61-P11
x-frame-options
DENY
GET
H3
200
World-Bank-logo-300x157.webp
www.givedirectly.org/wp-content/uploads/2023/10/
4 KB
4 KB
214ms
210ms
Image
image/webp
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/uploads/2023/10/World-Bank-logo-300x157.webp
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
32c7feeabbc5ff335db9b1c6c4a22b52cec693725f2506f75f08886aadbc5cb4
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
vary
Accept-Encoding
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
alt-svc
h3=":443"; ma=86400
x-cache
RefreshHit from cloudfront
content-length
3836
x-amz-cf-id
XNQr-gKMdYFNsaDTEP_77GYVhB58J5iRkYi-2caxFzNyLc4oEChCyg==
date
Sat, 12 Sep 2026 12:32:16 GMT
content-type
image/webp
last-modified
Mon, 07 Apr 2025 17:30:18 GMT
server
Apache/2.4.68 (Debian)
x-amz-cf-pop
IAD61-P11
x-frame-options
DENY
GET
H3
200
Community-engagement-event-in-Baiyeken-Maryland-300x225.png
www.givedirectly.org/wp-content/uploads/2024/03/
49 KB
49 KB
202ms
197ms
Image
image/png
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/uploads/2024/03/Community-engagement-event-in-Baiyeken-Maryland-300x225.png
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
48d92412103b1917917fad43511a9864e977f89423a823d94450bffa3ee6898d
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
vary
Accept-Encoding
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
alt-svc
h3=":443"; ma=86400
x-cache
RefreshHit from cloudfront
content-length
50296
x-amz-cf-id
RvEpeZW93HaiWD5x2bdwHaJkzhEQyDUbEUOS2xYHTE65C8yTSBUIxw==
date
Sat, 12 Sep 2026 12:32:16 GMT
content-type
image/png
last-modified
Mon, 07 Apr 2025 18:19:56 GMT
server
Apache/2.4.68 (Debian)
x-amz-cf-pop
IAD61-P11
x-frame-options
DENY
GET
H3
200
NEPI-enrollment-event-in-Monrovia-300x225.png
www.givedirectly.org/wp-content/uploads/2024/03/
30 KB
31 KB
260ms
256ms
Image
image/png
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/uploads/2024/03/NEPI-enrollment-event-in-Monrovia-300x225.png
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
b8564dc4cdc772344d2b96e0e0e7cd934d7d01793439edb5716cf5d1b879995d
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
alt-svc
h3=":443"; ma=86400
x-cache
Miss from cloudfront
content-length
31006
x-amz-cf-id
_eI_9u8uP7knOm1B06chjA7AWsWcPXEWUsNjtx5twA5-9AuFgE_xIQ==
date
Sat, 12 Sep 2026 12:32:16 GMT
content-type
image/png
last-modified
Mon, 07 Apr 2025 18:16:55 GMT
server
Apache/2.4.68 (Debian)
x-amz-cf-pop
IAD61-P11
x-frame-options
DENY
GET
H3
200
FSNR-recipient-registers-for-the-program-in-Nimba-County-300x225.png
www.givedirectly.org/wp-content/uploads/2024/03/
46 KB
46 KB
204ms
201ms
Image
image/png
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/uploads/2024/03/FSNR-recipient-registers-for-the-program-in-Nimba-County-300x225.png
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
8aec898354f84b41bf1d16161007cd4e617214da33db3b09f85e485e20374d61
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
vary
Accept-Encoding
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
alt-svc
h3=":443"; ma=86400
x-cache
RefreshHit from cloudfront
content-length
46625
x-amz-cf-id
Yv1K2AOKGx0oLwO_J9EUdYCEEabQu0pOabyY0L8Ej9AwVN_8bakzHg==
date
Sat, 12 Sep 2026 12:32:16 GMT
content-type
image/png
last-modified
Mon, 07 Apr 2025 18:17:28 GMT
server
Apache/2.4.68 (Debian)
x-amz-cf-pop
IAD61-P11
x-frame-options
DENY
GET
H3
200
Solomon-enrollment-300x225.png
www.givedirectly.org/wp-content/uploads/2024/03/
32 KB
33 KB
265ms
261ms
Image
image/png
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/uploads/2024/03/Solomon-enrollment-300x225.png
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
29d59026f0ea9a78effd5cb8a2d175865f2f045b9d49287c10cf443dbe8e4bbb
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
vary
Accept-Encoding
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
alt-svc
h3=":443"; ma=86400
x-cache
RefreshHit from cloudfront
content-length
33258
x-amz-cf-id
DOEp9PgDQ3Une1YBUMAt7WYbq45AiYbBg9gySbU78XqqTACJdctzag==
date
Sat, 12 Sep 2026 12:32:16 GMT
content-type
image/png
last-modified
Mon, 07 Apr 2025 18:19:20 GMT
server
Apache/2.4.68 (Debian)
x-amz-cf-pop
IAD61-P11
x-frame-options
DENY
GET
H3
200
Sarah-K-in-RiverGee-County-300x225.png
www.givedirectly.org/wp-content/uploads/2024/03/
31 KB
31 KB
264ms
261ms
Image
image/png
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/uploads/2024/03/Sarah-K-in-RiverGee-County-300x225.png
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
3a941464f4e01d9137623bb3a3f96edf759c910a6d282c4f1d59b56caaf40398
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
vary
Accept-Encoding
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
alt-svc
h3=":443"; ma=86400
x-cache
RefreshHit from cloudfront
content-length
31440
x-amz-cf-id
EbbTiPqGa6_mY6zPZ9xLOVmx1USX5c0UBL9zg80JdGQlgb_dPGFsMw==
date
Sat, 12 Sep 2026 12:32:16 GMT
content-type
image/png
last-modified
Mon, 07 Apr 2025 18:18:26 GMT
server
Apache/2.4.68 (Debian)
x-amz-cf-pop
IAD61-P11
x-frame-options
DENY
GET
H3
200
WASSCE-300x146.webp
www.givedirectly.org/wp-content/uploads/2024/03/
13 KB
14 KB
285ms
281ms
Image
image/webp
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/uploads/2024/03/WASSCE-300x146.webp
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
0fe8e60934edbcf8df2542daca0fa414584ccc54bcee57427a4da51dbc98df2e
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
vary
Accept-Encoding
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
alt-svc
h3=":443"; ma=86400
x-cache
RefreshHit from cloudfront
content-length
13696
x-amz-cf-id
tha6ewTKp4yg5o6VppOdWZCnYOuYpR3IbtuBSdYSIvfhry1sfXXuDg==
date
Sat, 12 Sep 2026 12:32:16 GMT
content-type
image/webp
last-modified
Mon, 07 Apr 2025 18:15:10 GMT
server
Apache/2.4.68 (Debian)
x-amz-cf-pop
IAD61-P11
x-frame-options
DENY
GET
H3
200
Program-pop-outs-300x225.png
www.givedirectly.org/wp-content/uploads/2024/03/
33 KB
33 KB
275ms
271ms
Image
image/png
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/uploads/2024/03/Program-pop-outs-300x225.png
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
ed01bb186cdaa0069b86a9e3f983af5ee155ffd95bfa07d028a079e4fa15e31d
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
vary
Accept-Encoding
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
alt-svc
h3=":443"; ma=86400
x-cache
RefreshHit from cloudfront
content-length
33892
x-amz-cf-id
SaARyUbC4PwVLthzb34jsYZh1CVRd9MqAibue_ZNcaMGCAoB14TPAg==
date
Sat, 12 Sep 2026 12:32:16 GMT
content-type
image/png
last-modified
Mon, 07 Apr 2025 18:17:16 GMT
server
Apache/2.4.68 (Debian)
x-amz-cf-pop
IAD61-P11
x-frame-options
DENY
GET
H3
200
website_pages.html Show response
donate.givedirectly.org/embed2/banners/
0
355 B
675ms
408ms
Fetch
text/html
18.238.49.55
Amazon.com
General
Full URL
https://donate.givedirectly.org/embed2/banners/website_pages.html?path=%2Fliberia
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
18.238.49.55 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-18-238-49-55.jfk52.r.cloudfront.net
Software
/ PHP/8.5.9
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=63115200; includeSubDomains; preload
X-Content-Type-Options nosniff
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-content-type-options
nosniff
alt-svc
h3=":443"; ma=86400
x-cache
Miss from cloudfront
x-amz-cf-id
LSccjovhEKlBDfZCGpk4hxTweDtxT9afcYk5TQEq5zmc8DKzJeooTg==
date
Sat, 12 Sep 2026 12:32:17 GMT
content-type
text/html; charset=utf-8
vary
CloudFront-Viewer-Country, Origin
x-frame-options
DENY
strict-transport-security
max-age=63115200; includeSubDomains; preload
cache-control
no-cache, private
referrer-policy
no-referrer
via
1.1 7933995c46b01504206ecd6d3dfa5d10.cloudfront.net (CloudFront)
access-control-allow-origin
https://www.givedirectly.org
content-length
0
x-amz-cf-pop
JFK52-P3
x-powered-by
PHP/8.5.9
GET
H3
200
World-Bank-logo-2048x1073.webp
www.givedirectly.org/wp-content/uploads/2023/10/
27 KB
27 KB
259ms
258ms
Image
image/webp
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/uploads/2023/10/World-Bank-logo-2048x1073.webp
Requested by
Host: ajax.googleapis.com
URL: https://ajax.googleapis.com/ajax/libs/jquery/3.7.0/jquery.min.js?ver=1787903358
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
83346941cce56b0970f9ea40ab23b100df1a123c1c0b1d33ab7fc062fba40767
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
vary
Accept-Encoding
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
alt-svc
h3=":443"; ma=86400
x-cache
RefreshHit from cloudfront
content-length
27604
x-amz-cf-id
9GAmi_BnxYANSIfLK1bv9rHIotr-Y83Gf5jslf33Ci37j4XjyQlbpw==
date
Sat, 12 Sep 2026 12:32:16 GMT
content-type
image/webp
last-modified
Mon, 07 Apr 2025 17:32:23 GMT
server
Apache/2.4.68 (Debian)
x-amz-cf-pop
IAD61-P11
x-frame-options
DENY
GET
H3
200
RTI-International-Logo.png
www.givedirectly.org/wp-content/uploads/2024/03/
13 KB
13 KB
241ms
240ms
Image
image/png
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/uploads/2024/03/RTI-International-Logo.png
Requested by
Host: ajax.googleapis.com
URL: https://ajax.googleapis.com/ajax/libs/jquery/3.7.0/jquery.min.js?ver=1787903358
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
66f0389d96a9067eb312d1307dbbecaba0ca19011d387de0f0e7e19acb993bc4
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
vary
Accept-Encoding
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
alt-svc
h3=":443"; ma=86400
x-cache
RefreshHit from cloudfront
content-length
12846
x-amz-cf-id
9KiziwWxHFl6Ew5eWj9Ri5Nxe-2hsiepCbsewM2AeJF7QJwkRYE-fQ==
date
Sat, 12 Sep 2026 12:32:16 GMT
content-type
image/png
last-modified
Mon, 07 Apr 2025 18:18:07 GMT
server
Apache/2.4.68 (Debian)
x-amz-cf-pop
IAD61-P11
x-frame-options
DENY
GET
H3
200
network-for-empowerment-progressive-initiatives-logo.png
www.givedirectly.org/wp-content/uploads/2024/03/
49 KB
49 KB
285ms
285ms
Image
image/png
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/uploads/2024/03/network-for-empowerment-progressive-initiatives-logo.png
Requested by
Host: ajax.googleapis.com
URL: https://ajax.googleapis.com/ajax/libs/jquery/3.7.0/jquery.min.js?ver=1787903358
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
41e9a6b19ec412ee545368d266fcea578cb95540a55cde8e743000b0f7b28fdc
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
vary
Accept-Encoding
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
alt-svc
h3=":443"; ma=86400
x-cache
RefreshHit from cloudfront
content-length
49696
x-amz-cf-id
dKBwyQOyQHourLziJYxrRAQWq5av0fpUo5wi4-fyy5qK0pez0tjfKA==
date
Sat, 12 Sep 2026 12:32:16 GMT
content-type
image/png
last-modified
Mon, 07 Apr 2025 18:16:31 GMT
server
Apache/2.4.68 (Debian)
x-amz-cf-pop
IAD61-P11
x-frame-options
DENY
GET
H3
200
King-Philanthropies-Logo-jpg.webp
www.givedirectly.org/wp-content/uploads/2024/03/
14 KB
14 KB
279ms
278ms
Image
image/webp
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/uploads/2024/03/King-Philanthropies-Logo-jpg.webp
Requested by
Host: ajax.googleapis.com
URL: https://ajax.googleapis.com/ajax/libs/jquery/3.7.0/jquery.min.js?ver=1787903358
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
f5b96378649f8a8c7e7e2ee18beafbf373b305acb34dd73be52682b08f48b6de
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
vary
Accept-Encoding
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
alt-svc
h3=":443"; ma=86400
x-cache
RefreshHit from cloudfront
content-length
14214
x-amz-cf-id
HD-0ocL2_ZE3I28JDPUogCUV2Xdx6dpBXu3zSf-RN656mNHHjb9s_A==
date
Sat, 12 Sep 2026 12:32:16 GMT
content-type
image/webp
last-modified
Mon, 07 Apr 2025 18:14:57 GMT
server
Apache/2.4.68 (Debian)
x-amz-cf-pop
IAD61-P11
x-frame-options
DENY
GET
H3
200
Liberia-Ministry-of-Gender-logo.png
www.givedirectly.org/wp-content/uploads/2024/03/
32 KB
32 KB
260ms
259ms
Image
image/png
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/uploads/2024/03/Liberia-Ministry-of-Gender-logo.png
Requested by
Host: ajax.googleapis.com
URL: https://ajax.googleapis.com/ajax/libs/jquery/3.7.0/jquery.min.js?ver=1787903358
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
90de1f3d11a5a315fe41d6d87a897bd2f8f3bdc836eac6040f19649e49ac1adb
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
vary
Accept-Encoding
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
alt-svc
h3=":443"; ma=86400
x-cache
RefreshHit from cloudfront
content-length
32727
x-amz-cf-id
tVzcUyCly2lkW0oiXX0YOqYe8Aku9abICfRxoPnXU465mzgGWlEhOQ==
date
Sat, 12 Sep 2026 12:32:16 GMT
content-type
image/png
last-modified
Mon, 07 Apr 2025 18:19:02 GMT
server
Apache/2.4.68 (Debian)
x-amz-cf-pop
IAD61-P11
x-frame-options
DENY
GET
H3
200
arrow-left-home.svg
www.givedirectly.org/wp-content/themes/givedirectly/img/icons/
1 KB
858 B
131ms
130ms
Image
image/svg+xml
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/themes/givedirectly/img/icons/arrow-left-home.svg
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/wp-content/themes/givedirectly/css/styles.min.css?ver=1787903358
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
fd9f80224f30051fc4480a89d25c328781f3de66f17d8624037977f65c8e7fcf
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/wp-content/themes/givedirectly/css/styles.min.css?ver=1787903358
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
vary
Accept-Encoding
cache-control
public, max-age=60, stale-while-revalidate=300
content-encoding
br
age
211
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
alt-svc
h3=":443"; ma=86400
x-cache
Hit from cloudfront
x-amz-cf-id
i05RZ42bG7Cr6y5ATf4FEdP_CvsN9GP_Fa-Y9eKjEJIJyry20JFh9g==
date
Sat, 12 Sep 2026 12:28:45 GMT
content-type
image/svg+xml
last-modified
Fri, 28 Aug 2026 07:48:46 GMT
server
Apache/2.4.68 (Debian)
x-amz-cf-pop
IAD61-P11
x-frame-options
DENY
GET
H3
200
arrow-right-home.svg
www.givedirectly.org/wp-content/themes/givedirectly/img/icons/
1 KB
872 B
135ms
134ms
Image
image/svg+xml
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/themes/givedirectly/img/icons/arrow-right-home.svg
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/wp-content/themes/givedirectly/css/styles.min.css?ver=1787903358
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
20b25217b834eba7ea0d181ff947366a220af18719c76e19ac66672d63d95cd8
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/wp-content/themes/givedirectly/css/styles.min.css?ver=1787903358
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
vary
Accept-Encoding
cache-control
public, max-age=60, stale-while-revalidate=300
content-encoding
br
age
211
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
alt-svc
h3=":443"; ma=86400
x-cache
Hit from cloudfront
x-amz-cf-id
I6-WHD0VDmsG8Dl3qcXkFb63ICoSzVxQvlyOxymt1U6tLGfczz8PPA==
date
Sat, 12 Sep 2026 12:28:45 GMT
content-type
image/svg+xml
last-modified
Fri, 28 Aug 2026 07:48:46 GMT
server
Apache/2.4.68 (Debian)
x-amz-cf-pop
IAD61-P11
x-frame-options
DENY
GET
DATA
200
OK
truncated
/
177 B
0
Image
image/svg+xml

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
d692a67352a3dfa80010c86a62761cfff05c0b1086618106a8576cc45a6a8115

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/svg+xml
GET
DATA
200
OK
truncated
/
515 B
0
Image
image/svg+xml

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
11ec04e3948e25a0d78d2f77c04940b8e38a086624ec36fa4605a2a69b133e94

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/svg+xml
GET
DATA
200
OK
truncated
/
242 B
0
Image
image/svg+xml

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
1f4513a435d6a3047d20a50c1e7d4263de42146c74be227f774b5e82e6357e75

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/svg+xml
GET
H3
200
USAID-logo-20230517.svg
www.givedirectly.org/wp-content/uploads/2023/05/
353 KB
0
0ms
0ms
Image
image/svg+xml
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/uploads/2023/05/USAID-logo-20230517.svg
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
f8a26c88ffc70bb0b322ae2df632fbbaaafeec0702b2e808fd8b5358fd8880a8
Security Headers
Name Value
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
cache-control
public, max-age=60, stale-while-revalidate=300
content-encoding
br
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
alt-svc
h3=":443"; ma=86400
x-cache
RefreshHit from cloudfront
x-amz-cf-id
Avdc_diZqBm1FQFyfyf6j1L8v9kZHYMYmzFAZWldxEJ-UdGBsg_fOw==
date
Sat, 12 Sep 2026 12:32:15 GMT
content-type
image/svg+xml
x-amz-cf-pop
IAD61-P11
server
Apache/2.4.68 (Debian)
last-modified
Mon, 07 Apr 2025 17:16:31 GMT
x-frame-options
DENY
GET
H3
200
Helena-in-Maryland-1-300x225.png
www.givedirectly.org/wp-content/uploads/2024/03/
45 KB
45 KB
247ms
247ms
Image
image/png
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/uploads/2024/03/Helena-in-Maryland-1-300x225.png
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
89f55bf8dd225e51c1e21e7ca14b27aa21585b36ccf83073295c2468b15390da
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
vary
Accept-Encoding
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
alt-svc
h3=":443"; ma=86400
x-cache
RefreshHit from cloudfront
content-length
46048
x-amz-cf-id
2tAi447yBrSb6AoHU4WwV_F9z_0C69aig6oy7Os7xGOIPjB3LjjevQ==
date
Sat, 12 Sep 2026 12:32:16 GMT
content-type
image/png
last-modified
Mon, 07 Apr 2025 18:18:05 GMT
server
Apache/2.4.68 (Debian)
x-amz-cf-pop
IAD61-P11
x-frame-options
DENY
GET
H3
200
script.js
www.givedirectly.org/wp-content/themes/givedirectly/blocks/gd-show-more/wrapper/
353 B
276 B
131ms
130ms
Other
text/javascript
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/themes/givedirectly/blocks/gd-show-more/wrapper/script.js?ver=0.1
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
0f0024b428a219528079eb53d4a21f8e1b8893d0bec5bdfadb24e7fffb3954ec
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
age
212
alt-svc
h3=":443"; ma=86400
x-cache
Hit from cloudfront
x-amz-cf-id
HlkA34oHSnCyTtwuQgvkL7WL4FH1izzxSiFOE64S2lZAFne2JGTNYQ==
date
Sat, 12 Sep 2026 12:32:16 GMT
last-modified
Fri, 28 Aug 2026 07:48:46 GMT
vary
Accept-Encoding
content-type
text/javascript
x-frame-options
DENY
strict-transport-security
max-age=31536000
cache-control
public, max-age=60, stale-while-revalidate=300
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
accept-ranges
bytes
content-length
202
x-amz-cf-pop
IAD61-P11
server
Apache/2.4.68 (Debian)
POST
H3
202
log-arrival
www.givedirectly.org/backend/
8 B
6 KB
384ms
384ms
Ping
text/html
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/backend/log-arrival
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
/ PHP/8.5.9
Resource Hash
954899c87da3edf57f4a4ebcf228972d176df05e1ff9f0cb212eda0b906eae97
Security Headers
Name Value
Content-Security-Policy script-src 'self' 'nonce-iGyei7u9Z3JFrLQ7OyvYzQeGUeafxQulWr0Wq6dy' *.js.stripe.com js.stripe.com maps.googleapis.com erinaceus.givedirectly.org www.googleadservices.com www.googletagmanager.com connect.facebook.net snap.licdn.com; style-src 'self' 'nonce-iGyei7u9Z3JFrLQ7OyvYzQeGUeafxQulWr0Wq6dy' *.typekit.net fonts.googleapis.com doublethedonation.com cdn.jsdelivr.net; img-src 'self' *.givedirectly.org *.devdirectly.org doublethedonation.com cdn.jsdelivr.net *.ytimg.com www.googletagmanager.com googleads.g.doubleclick.net stats.g.doubleclick.net www.googleadservices.com *.google.com *.google.ad *.google.ae *.google.com.af *.google.com.ag *.google.al *.google.am *.google.co.ao *.google.com.ar *.google.as *.google.at *.google.com.au *.google.az *.google.ba *.google.com.bd *.google.be *.google.bf *.google.bg *.google.com.bh *.google.bi *.google.bj *.google.com.bn *.google.com.bo *.google.com.br *.google.bs *.google.bt *.google.co.bw *.google.by *.google.com.bz *.google.ca *.google.cd *.google.cf *.google.cg *.google.ch *.google.ci *.google.co.ck *.google.cl *.google.cm *.google.cn *.google.com.co *.google.co.cr *.google.com.cu *.google.cv *.google.com.cy *.google.cz *.google.de *.google.dj *.google.dk *.google.dm *.google.com.do *.google.dz *.google.com.ec *.google.ee *.google.com.eg *.google.es *.google.com.et *.google.fi *.google.com.fj *.google.fm *.google.fr *.google.ga *.google.ge *.google.gg *.google.com.gh *.google.com.gi *.google.gl *.google.gm *.google.gr *.google.com.gt *.google.gy *.google.com.hk *.google.hn *.google.hr *.google.ht *.google.hu *.google.co.id *.google.ie *.google.co.il *.google.im *.google.co.in *.google.iq *.google.is *.google.it *.google.je *.google.com.jm *.google.jo *.google.co.jp *.google.co.ke *.google.com.kh *.google.ki *.google.kg *.google.co.kr *.google.com.kw *.google.kz *.google.la *.google.com.lb *.google.li *.google.lk *.google.co.ls *.google.lt *.google.lu *.google.lv *.google.com.ly *.google.co.ma *.google.md *.google.me *.google.mg *.google.mk *.google.ml *.google.com.mm *.google.mn *.google.com.mt *.google.mu *.google.mv *.google.mw *.google.com.mx *.google.com.my *.google.co.mz *.google.com.na *.google.com.ng *.google.com.ni *.google.ne *.google.nl *.google.no *.google.com.np *.google.nr *.google.nu *.google.co.nz *.google.com.om *.google.com.pa *.google.com.pe *.google.com.pg *.google.com.ph *.google.com.pk *.google.pl *.google.pn *.google.com.pr *.google.ps *.google.pt *.google.com.py *.google.com.qa *.google.ro *.google.ru *.google.rw *.google.com.sa *.google.com.sb *.google.sc *.google.se *.google.com.sg *.google.sh *.google.si *.google.sk *.google.com.sl *.google.sn *.google.so *.google.sm *.google.sr *.google.st *.google.com.sv *.google.td *.google.tg *.google.co.th *.google.com.tj *.google.tl *.google.tm *.google.tn *.google.to *.google.com.tr *.google.tt *.google.com.tw *.google.co.tz *.google.com.ua *.google.co.ug *.google.co.uk *.google.com.uy *.google.co.uz *.google.com.vc *.google.co.ve *.google.co.vi *.google.com.vn *.google.vu *.google.ws *.google.rs *.google.co.za *.google.co.zm *.google.co.zw *.google.cat www.facebook.com *.ads.linkedin.com; font-src 'self' *.typekit.net fonts.gstatic.com doublethedonation.com; connect-src 'self' api.stripe.com maps.googleapis.com erinaceus.givedirectly.org doublethedonation.com browser-intake-datadoghq.com *.analytics.google.com analytics.google.com *.google-analytics.com *.doubleclick.net www.googletagmanager.com www.googleadservices.com *.google.com *.google.ad *.google.ae *.google.com.af *.google.com.ag *.google.al *.google.am *.google.co.ao *.google.com.ar *.google.as *.google.at *.google.com.au *.google.az *.google.ba *.google.com.bd *.google.be *.google.bf *.google.bg *.google.com.bh *.google.bi *.google.bj *.google.com.bn *.google.com.bo *.google.com.br *.google.bs *.google.bt *.google.co.bw *.google.by *.google.com.bz *.google.ca *.google.cd *.google.cf *.google.cg *.google.ch *.google.ci *.google.co.ck *.google.cl *.google.cm *.google.cn *.google.com.co *.google.co.cr *.google.com.cu *.google.cv *.google.com.cy *.google.cz *.google.de *.google.dj *.google.dk *.google.dm *.google.com.do *.google.dz *.google.com.ec *.google.ee *.google.com.eg *.google.es *.google.com.et *.google.fi *.google.com.fj *.google.fm *.google.fr *.google.ga *.google.ge *.google.gg *.google.com.gh *.google.com.gi *.google.gl *.google.gm *.google.gr *.google.com.gt *.google.gy *.google.com.hk *.google.hn *.google.hr *.google.ht *.google.hu *.google.co.id *.google.ie *.google.co.il *.google.im *.google.co.in *.google.iq *.google.is *.google.it *.google.je *.google.com.jm *.google.jo *.google.co.jp *.google.co.ke *.google.com.kh *.google.ki *.google.kg *.google.co.kr *.google.com.kw *.google.kz *.google.la *.google.com.lb *.google.li *.google.lk *.google.co.ls *.google.lt *.google.lu *.google.lv *.google.com.ly *.google.co.ma *.google.md *.google.me *.google.mg *.google.mk *.google.ml *.google.com.mm *.google.mn *.google.com.mt *.google.mu *.google.mv *.google.mw *.google.com.mx *.google.com.my *.google.co.mz *.google.com.na *.google.com.ng *.google.com.ni *.google.ne *.google.nl *.google.no *.google.com.np *.google.nr *.google.nu *.google.co.nz *.google.com.om *.google.com.pa *.google.com.pe *.google.com.pg *.google.com.ph *.google.com.pk *.google.pl *.google.pn *.google.com.pr *.google.ps *.google.pt *.google.com.py *.google.com.qa *.google.ro *.google.ru *.google.rw *.google.com.sa *.google.com.sb *.google.sc *.google.se *.google.com.sg *.google.sh *.google.si *.google.sk *.google.com.sl *.google.sn *.google.so *.google.sm *.google.sr *.google.st *.google.com.sv *.google.td *.google.tg *.google.co.th *.google.com.tj *.google.tl *.google.tm *.google.tn *.google.to *.google.com.tr *.google.tt *.google.com.tw *.google.co.tz *.google.com.ua *.google.co.ug *.google.co.uk *.google.com.uy *.google.co.uz *.google.com.vc *.google.co.ve *.google.co.vi *.google.com.vn *.google.vu *.google.ws *.google.rs *.google.co.za *.google.co.zm *.google.co.zw *.google.cat www.facebook.com *.ads.linkedin.com; frame-src 'self' *.js.stripe.com js.stripe.com hooks.stripe.com youtube.com *.youtube.com ourworldindata.org *.googletagmanager.com *.doubleclick.net www.facebook.com; frame-ancestors 'none';

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

content-security-policy
script-src 'self' 'nonce-iGyei7u9Z3JFrLQ7OyvYzQeGUeafxQulWr0Wq6dy' *.js.stripe.com js.stripe.com maps.googleapis.com erinaceus.givedirectly.org www.googleadservices.com www.googletagmanager.com connect.facebook.net snap.licdn.com; style-src 'self' 'nonce-iGyei7u9Z3JFrLQ7OyvYzQeGUeafxQulWr0Wq6dy' *.typekit.net fonts.googleapis.com doublethedonation.com cdn.jsdelivr.net; img-src 'self' *.givedirectly.org *.devdirectly.org doublethedonation.com cdn.jsdelivr.net *.ytimg.com www.googletagmanager.com googleads.g.doubleclick.net stats.g.doubleclick.net www.googleadservices.com *.google.com *.google.ad *.google.ae *.google.com.af *.google.com.ag *.google.al *.google.am *.google.co.ao *.google.com.ar *.google.as *.google.at *.google.com.au *.google.az *.google.ba *.google.com.bd *.google.be *.google.bf *.google.bg *.google.com.bh *.google.bi *.google.bj *.google.com.bn *.google.com.bo *.google.com.br *.google.bs *.google.bt *.google.co.bw *.google.by *.google.com.bz *.google.ca *.google.cd *.google.cf *.google.cg *.google.ch *.google.ci *.google.co.ck *.google.cl *.google.cm *.google.cn *.google.com.co *.google.co.cr *.google.com.cu *.google.cv *.google.com.cy *.google.cz *.google.de *.google.dj *.google.dk *.google.dm *.google.com.do *.google.dz *.google.com.ec *.google.ee *.google.com.eg *.google.es *.google.com.et *.google.fi *.google.com.fj *.google.fm *.google.fr *.google.ga *.google.ge *.google.gg *.google.com.gh *.google.com.gi *.google.gl *.google.gm *.google.gr *.google.com.gt *.google.gy *.google.com.hk *.google.hn *.google.hr *.google.ht *.google.hu *.google.co.id *.google.ie *.google.co.il *.google.im *.google.co.in *.google.iq *.google.is *.google.it *.google.je *.google.com.jm *.google.jo *.google.co.jp *.google.co.ke *.google.com.kh *.google.ki *.google.kg *.google.co.kr *.google.com.kw *.google.kz *.google.la *.google.com.lb *.google.li *.google.lk *.google.co.ls *.google.lt *.google.lu *.google.lv *.google.com.ly *.google.co.ma *.google.md *.google.me *.google.mg *.google.mk *.google.ml *.google.com.mm *.google.mn *.google.com.mt *.google.mu *.google.mv *.google.mw *.google.com.mx *.google.com.my *.google.co.mz *.google.com.na *.google.com.ng *.google.com.ni *.google.ne *.google.nl *.google.no *.google.com.np *.google.nr *.google.nu *.google.co.nz *.google.com.om *.google.com.pa *.google.com.pe *.google.com.pg *.google.com.ph *.google.com.pk *.google.pl *.google.pn *.google.com.pr *.google.ps *.google.pt *.google.com.py *.google.com.qa *.google.ro *.google.ru *.google.rw *.google.com.sa *.google.com.sb *.google.sc *.google.se *.google.com.sg *.google.sh *.google.si *.google.sk *.google.com.sl *.google.sn *.google.so *.google.sm *.google.sr *.google.st *.google.com.sv *.google.td *.google.tg *.google.co.th *.google.com.tj *.google.tl *.google.tm *.google.tn *.google.to *.google.com.tr *.google.tt *.google.com.tw *.google.co.tz *.google.com.ua *.google.co.ug *.google.co.uk *.google.com.uy *.google.co.uz *.google.com.vc *.google.co.ve *.google.co.vi *.google.com.vn *.google.vu *.google.ws *.google.rs *.google.co.za *.google.co.zm *.google.co.zw *.google.cat www.facebook.com *.ads.linkedin.com; font-src 'self' *.typekit.net fonts.gstatic.com doublethedonation.com; connect-src 'self' api.stripe.com maps.googleapis.com erinaceus.givedirectly.org doublethedonation.com browser-intake-datadoghq.com *.analytics.google.com analytics.google.com *.google-analytics.com *.doubleclick.net www.googletagmanager.com www.googleadservices.com *.google.com *.google.ad *.google.ae *.google.com.af *.google.com.ag *.google.al *.google.am *.google.co.ao *.google.com.ar *.google.as *.google.at *.google.com.au *.google.az *.google.ba *.google.com.bd *.google.be *.google.bf *.google.bg *.google.com.bh *.google.bi *.google.bj *.google.com.bn *.google.com.bo *.google.com.br *.google.bs *.google.bt *.google.co.bw *.google.by *.google.com.bz *.google.ca *.google.cd *.google.cf *.google.cg *.google.ch *.google.ci *.google.co.ck *.google.cl *.google.cm *.google.cn *.google.com.co *.google.co.cr *.google.com.cu *.google.cv *.google.com.cy *.google.cz *.google.de *.google.dj *.google.dk *.google.dm *.google.com.do *.google.dz *.google.com.ec *.google.ee *.google.com.eg *.google.es *.google.com.et *.google.fi *.google.com.fj *.google.fm *.google.fr *.google.ga *.google.ge *.google.gg *.google.com.gh *.google.com.gi *.google.gl *.google.gm *.google.gr *.google.com.gt *.google.gy *.google.com.hk *.google.hn *.google.hr *.google.ht *.google.hu *.google.co.id *.google.ie *.google.co.il *.google.im *.google.co.in *.google.iq *.google.is *.google.it *.google.je *.google.com.jm *.google.jo *.google.co.jp *.google.co.ke *.google.com.kh *.google.ki *.google.kg *.google.co.kr *.google.com.kw *.google.kz *.google.la *.google.com.lb *.google.li *.google.lk *.google.co.ls *.google.lt *.google.lu *.google.lv *.google.com.ly *.google.co.ma *.google.md *.google.me *.google.mg *.google.mk *.google.ml *.google.com.mm *.google.mn *.google.com.mt *.google.mu *.google.mv *.google.mw *.google.com.mx *.google.com.my *.google.co.mz *.google.com.na *.google.com.ng *.google.com.ni *.google.ne *.google.nl *.google.no *.google.com.np *.google.nr *.google.nu *.google.co.nz *.google.com.om *.google.com.pa *.google.com.pe *.google.com.pg *.google.com.ph *.google.com.pk *.google.pl *.google.pn *.google.com.pr *.google.ps *.google.pt *.google.com.py *.google.com.qa *.google.ro *.google.ru *.google.rw *.google.com.sa *.google.com.sb *.google.sc *.google.se *.google.com.sg *.google.sh *.google.si *.google.sk *.google.com.sl *.google.sn *.google.so *.google.sm *.google.sr *.google.st *.google.com.sv *.google.td *.google.tg *.google.co.th *.google.com.tj *.google.tl *.google.tm *.google.tn *.google.to *.google.com.tr *.google.tt *.google.com.tw *.google.co.tz *.google.com.ua *.google.co.ug *.google.co.uk *.google.com.uy *.google.co.uz *.google.com.vc *.google.co.ve *.google.co.vi *.google.com.vn *.google.vu *.google.ws *.google.rs *.google.co.za *.google.co.zm *.google.co.zw *.google.cat www.facebook.com *.ads.linkedin.com; frame-src 'self' *.js.stripe.com js.stripe.com hooks.stripe.com youtube.com *.youtube.com ourworldindata.org *.googletagmanager.com *.doubleclick.net www.facebook.com; frame-ancestors 'none';
cache-control
no-cache, private
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
alt-svc
h3=":443"; ma=86400
x-cache
Miss from cloudfront
content-length
8
x-amz-cf-id
uO20BmzANcC8NKsj9wwPR7rpODrnOjY-yZEfL7eeQNVYzD4qQZnM0A==
date
Sat, 12 Sep 2026 12:32:16 GMT
content-type
text/html; charset=utf-8
x-powered-by
PHP/8.5.9
x-amz-cf-pop
IAD61-P11
GET
H3
200
config.js Show response
erinaceus.givedirectly.org/array/phc_j1Fm3HqKiplMs7guXcEKIdcYC8CQCUOu31quq5YpXFj/
3 KB
2 KB
143ms
143ms
Script
application/javascript
3.167.69.84
Amazon.com
General
Full URL
https://erinaceus.givedirectly.org/array/phc_j1Fm3HqKiplMs7guXcEKIdcYC8CQCUOu31quq5YpXFj/config.js
Requested by
Host: erinaceus.givedirectly.org
URL: https://erinaceus.givedirectly.org/static/array.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
3.167.69.84 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-167-69-84.iad61.r.cloudfront.net
Software
envoy /
Resource Hash
af5095668b522414e145df421c68f974dd4c9484c43a5f0884633458cb38bbd2
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 1; mode=block

Request headers

Origin
https://www.givedirectly.org
sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-content-type-options
nosniff
x-cache
Miss from cloudfront
x-amz-cf-id
Gmg72s4MlGMrLACkZDqlx69HKbzceLZBYeXc1drDqn5033ZDNSbNYA==
date
Sat, 12 Sep 2026 12:32:17 GMT
content-type
application/javascript
vary
Origin,origin,Accept-Encoding
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=31536000; includeSubDomains
cache-control
public, max-age=300
x-envoy-upstream-service-time
1
access-control-allow-credentials
true
referrer-policy
strict-origin-when-cross-origin
via
1.1 cf8c5b66c93d44ff2109ede7dd215622.cloudfront.net (CloudFront)
access-control-allow-origin
https://www.givedirectly.org
x-xss-protection
1; mode=block
x-amz-cf-pop
IAD61-P6
server
envoy
GET
H2
200
www-player.css
www.youtube.com/s/player/8c3fda2d/ Frame 0D77
531 KB
57 KB
93ms
91ms
Stylesheet
text/css
142.251.153.4
Google LLC
General
Full URL
https://www.youtube.com/s/player/8c3fda2d/www-player.css
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/mCsv_yLgi3c?start=1&feature=oembed
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.153.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
1e6f131e5c23998532caa01dec741cd746efdb7364cffaf33a43f227aaa0d458
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/mCsv_yLgi3c?start=1&feature=oembed
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
25285
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Sun, 12 Sep 2027 05:30:52 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sat, 12 Sep 2026 05:30:52 GMT
last-modified
Mon, 07 Sep 2026 04:37:27 GMT
content-type
text/css
vary
Accept-Encoding, Origin
cache-control
public, max-age=31536000
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
58390
x-xss-protection
0
server
sffe
GET
H2
200
m=root,base
www.youtube.com/s/_/ytembeds/_/ss/k=ytembeds.base.HY7wD9GGp-g.L.W.O/am=AAAAQA/d=1/br=1/rs=AGKMywE4Kjs9hFDhD74lwcLYIXdA_OMvQQ/ Frame 0D77
0
409 B
140ms
139ms
Stylesheet
text/css
142.251.153.4
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/ss/k=ytembeds.base.HY7wD9GGp-g.L.W.O/am=AAAAQA/d=1/br=1/rs=AGKMywE4Kjs9hFDhD74lwcLYIXdA_OMvQQ/m=root,base
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/mCsv_yLgi3c?start=1&feature=oembed
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.153.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/mCsv_yLgi3c?start=1&feature=oembed
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

age
84965
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Sat, 11 Sep 2027 12:56:12 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 11 Sep 2026 12:56:12 GMT
last-modified
Fri, 11 Sep 2026 03:12:40 GMT
content-type
text/css; charset=UTF-8
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
0
x-xss-protection
0
server
sffe
GET
H3
200
KFO7CnqEu92Fr1ME7kSn66aGLdTylUAMa3yUBA.woff2
fonts.gstatic.com/s/roboto/v48/ Frame 0D77
39 KB
39 KB
252ms
121ms
Font
font/woff2
142.250.31.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/roboto/v48/KFO7CnqEu92Fr1ME7kSn66aGLdTylUAMa3yUBA.woff2
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/mCsv_yLgi3c?start=1&feature=oembed
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.250.31.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bj-in-f94.1e100.net
Software
sffe /
Resource Hash
20b535fa80c8189e3b87d1803038389960203a886d502bc2ef1857affc2f38d2
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://www.youtube.com
sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

age
3994
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Sun, 12 Sep 2027 11:25:43 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sat, 12 Sep 2026 11:25:43 GMT
last-modified
Thu, 29 May 2025 23:30:55 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
40128
x-xss-protection
0
server
sffe
GET

m=root,base
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywHdVJjs6ktwWXG8Pg3CpN4ZEVjBaQ/ Frame 0D77
0
0


GET
H3
200
base.js Show response
www.youtube.com/s/player/8c3fda2d/player_embed_es6.vflset/en_US/ Frame 0D77
2 MB
472 KB
66ms
64ms
Script
text/javascript
142.251.153.4
Google LLC
General
Full URL
https://www.youtube.com/s/player/8c3fda2d/player_embed_es6.vflset/en_US/base.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/mCsv_yLgi3c?start=1&feature=oembed
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.153.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
9d66ed39cd90111abe8be07798b65f01076983dcead837eada3c68219e1cd383
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/mCsv_yLgi3c?start=1&feature=oembed
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
111207
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Sat, 11 Sep 2027 05:38:50 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 11 Sep 2026 05:38:50 GMT
last-modified
Mon, 07 Sep 2026 04:37:27 GMT
content-type
text/javascript
vary
Accept-Encoding, Origin
cache-control
public, max-age=31536000
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
483559
x-xss-protection
0
server
sffe
POST
H3
200
/ Show response
erinaceus.givedirectly.org/e/
15 B
397 B
165ms
165ms
Fetch
application/json
3.167.69.84
Amazon.com
General
Full URL
https://erinaceus.givedirectly.org/e/
Requested by
Host: erinaceus.givedirectly.org
URL: https://erinaceus.givedirectly.org/static/array.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
3.167.69.84 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-167-69-84.iad61.r.cloudfront.net
Software
envoy /
Resource Hash
0c40bafcfdc8adc6db63a6a5bfdb3dd5201798e6163fc674dc2fcbdb2a4134f1
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
content-type
text/plain
sec-ch-ua-mobile
?0

Response headers

x-content-type-options
nosniff
x-cache
Miss from cloudfront
x-amz-cf-id
MywVWBxbrpJbFLVMWiSNtP9XK5NThlTXSxBHP4hWxPwuPnc2GlzVhA==
date
Sat, 12 Sep 2026 12:32:17 GMT
content-type
application/json
vary
origin, access-control-request-method, access-control-request-headers
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=31536000; includeSubDomains
x-envoy-upstream-service-time
21
access-control-allow-credentials
true
referrer-policy
strict-origin-when-cross-origin
via
1.1 cf8c5b66c93d44ff2109ede7dd215622.cloudfront.net (CloudFront)
access-control-allow-origin
https://www.givedirectly.org
content-length
15
x-xss-protection
1; mode=block
x-amz-cf-pop
IAD61-P6
server
envoy
GET
H3
200
surveys.js Show response
erinaceus.givedirectly.org/static/1.430.2/
102 KB
34 KB
133ms
133ms
Script
application/javascript
3.167.69.84
Amazon.com
General
Full URL
https://erinaceus.givedirectly.org/static/1.430.2/surveys.js
Requested by
Host: erinaceus.givedirectly.org
URL: https://erinaceus.givedirectly.org/static/array.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
3.167.69.84 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-167-69-84.iad61.r.cloudfront.net
Software
cloudflare /
Resource Hash
9719b92698fc9da98e2054c27e8c540db6d375791d68c686d48f1fb8584886a9
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 1; mode=block

Request headers

Origin
https://www.givedirectly.org
sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
3000
access-control-expose-headers
ETag
content-encoding
br
cf-cache-status
MISS
etag
W/"8c132fedb7bbebf06dfb04291b2ee0de"
x-amz-version-id
Z4.wotP3aH8Dny3v4YFXwtDsbNE.ELfE
age
90212
access-control-allow-methods
POST, GET, DELETE, PUT
x-content-type-options
nosniff
x-cache
Hit from cloudfront
x-amz-cf-id
rueq1_hOy04tmx_lZTERsL-VPZxqQFZjsagcGrdtZK_2_b8uRLi5aA==
date
Fri, 11 Sep 2026 11:28:45 GMT
content-type
application/javascript
last-modified
Fri, 11 Sep 2026 09:21:47 GMT
vary
Origin
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=31536000
cache-control
public, max-age=31536000, immutable
referrer-policy
strict-origin-when-cross-origin
via
1.1 cf8c5b66c93d44ff2109ede7dd215622.cloudfront.net (CloudFront)
cf-ray
a39654adfd6ee5ed-IAD
access-control-allow-origin
*
x-xss-protection
1; mode=block
x-amz-cf-pop
IAD61-P6
server
cloudflare
x-amz-server-side-encryption
AES256
GET
H3
200
dead-clicks-autocapture.js Show response
erinaceus.givedirectly.org/static/1.430.2/
22 KB
9 KB
135ms
134ms
Script
application/javascript
3.167.69.84
Amazon.com
General
Full URL
https://erinaceus.givedirectly.org/static/1.430.2/dead-clicks-autocapture.js
Requested by
Host: erinaceus.givedirectly.org
URL: https://erinaceus.givedirectly.org/static/array.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
3.167.69.84 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-167-69-84.iad61.r.cloudfront.net
Software
cloudflare /
Resource Hash
44343d3cafbec3175a2ec435bdf729f169a1829a06e11a5fbdf1e8656eac2052
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 1; mode=block

Request headers

Origin
https://www.givedirectly.org
sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
3000
access-control-expose-headers
ETag
content-encoding
br
cf-cache-status
MISS
etag
W/"297d271cc6d79f33c150f0054412eaf9"
x-amz-version-id
VrJjvcGbwBiIDy1G4g7mm78JxXd1UVMn
age
90212
access-control-allow-methods
POST, GET, DELETE, PUT
x-content-type-options
nosniff
x-cache
Hit from cloudfront
x-amz-cf-id
9j8YZJMgLwImhFh5CzDbkF15UZBJCtuqvv9P6lJupLbwVFQ3JJVtbw==
date
Fri, 11 Sep 2026 11:28:45 GMT
content-type
application/javascript
last-modified
Fri, 11 Sep 2026 09:21:47 GMT
vary
Origin
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=31536000
cache-control
public, max-age=31536000, immutable
referrer-policy
strict-origin-when-cross-origin
via
1.1 cf8c5b66c93d44ff2109ede7dd215622.cloudfront.net (CloudFront)
cf-ray
a39654ae19dc379e-IAD
access-control-allow-origin
*
x-xss-protection
1; mode=block
x-amz-cf-pop
IAD61-P6
server
cloudflare
x-amz-server-side-encryption
AES256
POST
H3
200
/ Show response
erinaceus.givedirectly.org/flags/
4 KB
1 KB
144ms
143ms
Fetch
application/json
3.167.69.84
Amazon.com
General
Full URL
https://erinaceus.givedirectly.org/flags/?v=2
Requested by
Host: erinaceus.givedirectly.org
URL: https://erinaceus.givedirectly.org/static/array.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
3.167.69.84 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-167-69-84.iad61.r.cloudfront.net
Software
envoy /
Resource Hash
fe87d870bd269d4c16c574da5b843f13cbe4722fb824a87eb8b3a162c0330a26
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
content-type
text/plain
sec-ch-ua-mobile
?0

Response headers

access-control-expose-headers
x-posthog-rate-limit-warning
content-encoding
gzip
x-content-type-options
nosniff
x-cache
Miss from cloudfront
x-amz-cf-id
pjJDc6P8fkQJ51SrOyticdPYi7laKippzTqEAmRVYVnKn1RgBfVBSA==
date
Sat, 12 Sep 2026 12:32:17 GMT
content-type
application/json
vary
origin, access-control-request-method, access-control-request-headers, Accept-Encoding
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=31536000; includeSubDomains
x-envoy-upstream-service-time
3
access-control-allow-credentials
true
referrer-policy
strict-origin-when-cross-origin
via
1.1 cf8c5b66c93d44ff2109ede7dd215622.cloudfront.net (CloudFront)
access-control-allow-origin
https://www.givedirectly.org
x-xss-protection
1; mode=block
x-amz-cf-pop
IAD61-P6
server
envoy
GET
H2
200
insight.min.js Show response
snap.licdn.com/li.lms-analytics/
56 KB
20 KB
598ms
199ms
Script
application/javascript
23.55.176.231
AKAMAI-ASN1 Akama...
General
Full URL
https://snap.licdn.com/li.lms-analytics/insight.min.js
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtm.js?id=GTM-PJNMMGH
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
23.55.176.231 Ashburn, United States, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a23-55-176-231.deploy.static.akamaitechnologies.com
Software
/
Resource Hash
af0745562f1d597413e728a7ddaf2513e7385c4fa3a1ad800e8aa70128aad4cc
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=86400
content-encoding
gzip
x-cdn-proto
HTTP2
x-cdn
AKAM
x-content-type-options
nosniff
accept-ranges
bytes
alt-svc
h3=":443"; ma=93600,h3-29=":443"; ma=93600
access-control-allow-origin
*
content-length
20593
date
Sat, 12 Sep 2026 12:32:17 GMT
last-modified
Tue, 18 Aug 2026 09:14:54 GMT
content-type
application/javascript;charset=utf-8
vary
Accept-Encoding
x-amz-server-side-encryption
AES256
GET
H3
200
fbevents.js Show response
connect.facebook.net/en_US/
410 KB
108 KB
242ms
119ms
Script
application/x-javascript
57.144.70.128
Facebook
General
Full URL
https://connect.facebook.net/en_US/fbevents.js
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
57.144.70.128 Reston, United States, ASN32934 (FACEBOOK - Facebook, Inc., US),
Reverse DNS
xx-fbcdn-shv-01-xxc1.fbcdn.net
Software
/
Resource Hash
bd7f7c0f0d2c857c1981dae1c9224ba44a6e0c8baff8d2b0b30362694235b3ec
Security Headers
Name Value
Content-Security-Policy default-src *.facebook.com *.fbcdn.net *.facebook.net 'self' blob:;script-src *.facebook.com *.fbcdn.net *.facebook.net blob: 'self' 'nonce-SYLCjsMQ';style-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob: 'unsafe-inline';connect-src *.facebook.com facebook.com *.fbcdn.net *.facebook.net wss://*.facebook.com:* wss://*.fbcdn.net attachment.fbsbx.com *.cdninstagram.com blob: 'self' data: https://edge-chat.facebook.net https://edge-chat-latest.facebook.net wss://edge-chat-latest.facebook.net wss://edge-chat.facebook.net wss://edge-chat.socialplugin.facebook.net wss://edge-chat-latest.socialplugin.facebook.net https://edge-chat.socialplugin.facebook.net https://edge-chat-latest.socialplugin.facebook.net;font-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;img-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;media-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;child-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;frame-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;manifest-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;object-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;worker-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;block-all-mixed-content;upgrade-insecure-requests;
Strict-Transport-Security max-age=31536000; preload; includeSubDomains
X-Content-Type-Options nosniff
X-Frame-Options DENY
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
report-to
{"max_age":2592000,"endpoints":[{"url":"https:\/\/www.facebook.com\/browser_reporting\/coop\/?minimize=0"}],"group":"coop_report","include_subdomains":true}, {"max_age":86400,"endpoints":[{"url":"https:\/\/www.facebook.com\/browser_reporting\/coep\/?minimize=0"}],"group":"coep_report"}, {"max_age":21600,"endpoints":[{"url":"https:\/\/www.facebook.com\/ajax\/browser_error_reports\/"}],"group":"permissions_policy"}
x-content-type-options
nosniff
expires
Sat, 01 Jan 2000 00:00:00 GMT
alt-svc
h3=":443"; ma=86400
date
Sat, 12 Sep 2026 12:32:17 GMT
content-type
application/x-javascript; charset=utf-8
vary
Accept-Encoding
cross-origin-embedder-policy-report-only
require-corp;report-to="coep_report"
priority
u=3,i
x-frame-options
DENY
strict-transport-security
max-age=31536000; preload; includeSubDomains
reporting-endpoints
coop_report="https://www.facebook.com/browser_reporting/coop/?minimize=0", coep_report="https://www.facebook.com/browser_reporting/coep/?minimize=0", permissions_policy="https://www.facebook.com/ajax/browser_error_reports/"
content-security-policy
default-src *.facebook.com *.fbcdn.net *.facebook.net 'self' blob:;script-src *.facebook.com *.fbcdn.net *.facebook.net blob: 'self' 'nonce-SYLCjsMQ';style-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob: 'unsafe-inline';connect-src *.facebook.com facebook.com *.fbcdn.net *.facebook.net wss://*.facebook.com:* wss://*.fbcdn.net attachment.fbsbx.com *.cdninstagram.com blob: 'self' data: https://edge-chat.facebook.net https://edge-chat-latest.facebook.net wss://edge-chat-latest.facebook.net wss://edge-chat.facebook.net wss://edge-chat.socialplugin.facebook.net wss://edge-chat-latest.socialplugin.facebook.net https://edge-chat.socialplugin.facebook.net https://edge-chat-latest.socialplugin.facebook.net;font-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;img-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;media-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;child-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;frame-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;manifest-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;object-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;worker-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;block-all-mixed-content;upgrade-insecure-requests;
cache-control
public, max-age=1200
timing-allow-origin
*
cross-origin-opener-policy
same-origin-allow-popups
x-fb-connection-quality
GOOD; q=0.7, rtt=117, rtx=0, c=24, mss=1232, tbw=8785, tp=13, tpl=0, uplat=1, ullat=-1
pragma
public
x-fb-debug
XMihwtHv5zdb96tVp3Xnb9Mu5L92HNL+III51LFN2UIsYG0/xCPnx2wGfnFO/1LGBW3oY4Q31idLgOQQEzZ5UQ==
cross-origin-resource-policy
cross-origin
permissions-policy
accelerometer=(), attribution-reporting=(), autoplay=(), bluetooth=(), camera=(), ch-device-memory=(), ch-downlink=(), ch-dpr=(), ch-ect=(), ch-rtt=(), ch-save-data=(), ch-ua-arch=(), ch-ua-bitness=(), ch-viewport-height=(), ch-viewport-width=(), ch-width=(), clipboard-read=(), clipboard-write=(), compute-pressure=(), display-capture=(), encrypted-media=(), fullscreen=(self), gamepad=(), geolocation=(), gyroscope=(), hid=(), idle-detection=(), interest-cohort=(), keyboard-map=(), local-fonts=(), magnetometer=(), microphone=(), midi=(), otp-credentials=(), payment=(), picture-in-picture=(), private-state-token-issuance=(), publickey-credentials-get=(), screen-wake-lock=(), serial=(), shared-storage=(), shared-storage-select-url=(), private-state-token-redemption=(), usb=(), unload=(self), window-management=(), xr-spatial-tracking=();report-to="permissions_policy"
x-fb-optimizer
0
document-policy
force-load-at-top, include-js-call-stacks-in-crash-reports
content-length
110078
x-xss-protection
0
origin-agent-cluster
?1
GET
H2
200
ytc.js Show response
s.yimg.com/wi/
19 KB
7 KB
610ms
205ms
Script
application/javascript
69.147.92.11
Yahoo Holdings Inc.
General
Full URL
https://s.yimg.com/wi/ytc.js
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
69.147.92.11 Ashburn, United States, ASN14777 (YAHOO - Yahoo Holdings Inc., US),
Reverse DNS
e1.ycpi.vip.dca.yahoo.com
Software
ATS /
Resource Hash
9f17a11aa8e2908c07d47b7ce57df686a9cff242515da2f997d41147a8282b26
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
"b15749319e3de4e75b27beff49193136-df"
x-amz-version-id
wzcqbRPQhcYbsQujxcYK.rrDceEBX0AH
age
3285
x-content-type-options
nosniff
date
Sat, 12 Sep 2026 11:37:33 GMT
last-modified
Thu, 06 Aug 2026 09:14:34 GMT
vary
Accept-Encoding,Origin
x-amz-expiration
expiry-date="Sat, 11 Sep 2027 00:00:00 GMT", rule-id="standard-lifecycle"
content-type
application/javascript
x-amz-id-2
jvsg6fATWSsbWuLM1mQt/LbeVgj39ugvwcXl+SGVKMVbgBRCvnYL8g0shWiWiCCSYV2Fl+8iuXw=
strict-transport-security
max-age=31536000
cache-control
public,max-age=3600
ats-carp-promotion
1, 1
referrer-policy
no-referrer-when-downgrade
x-amz-request-id
ACZWY6TZHACB6BXB
accept-ranges
bytes
access-control-allow-origin
*
content-length
6812
server
ATS
POST
H3
200
collect
www.google.com/ccm/
0
0
135ms
67ms
Fetch
text/plain
142.251.151.119
Google LLC
General
Full URL
https://www.google.com/ccm/collect?rcb=19&frm=0&apvc=1&ae=g&auid=1823712742.1789216337&dt=Cash%20Aid%20in%20Liberia%20%7C%20GiveDirectly&en=page_view&dl=https%3A%2F%2Fwww.givedirectly.org%2Fliberia&scrsrc=www.googletagmanager.com&rnd=485911603.1789216337&navt=n&npa=0&ep.ads_data_redaction=0&gtm=45He6992v812195104za200zd812195104xea&gcd=13l3l3l3l1l1&dma=0&tag_exp=115938465~115938468~118131809~118897920~118897930~120385423~120469145~120469153~120847433&tft=1789216337412&tfd=6733&fmt=8
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtm.js?id=GTM-PJNMMGH
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.151.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
/
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

POST
H3
204
collect
ad.doubleclick.net/ccm/s/
0
0
261ms
137ms
Fetch
text/html
192.178.218.148
Google LLC
General
Full URL
https://ad.doubleclick.net/ccm/s/collect?auid=1823712742.1789216337&gtm=45He6992v812195104za200zd812195104xea&fmt=8
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtm.js?id=GTM-PJNMMGH
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
192.178.218.148 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
yuiadtq-in-f148.1e100.net
Software
/
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

GET
H2
200
js Show response
www.googletagmanager.com/gtag/
573 KB
184 KB
168ms
166ms
Script
application/javascript
142.251.179.97
Google LLC
General
Full URL
https://www.googletagmanager.com/gtag/js?id=G-GV8XF9FJ16&cx=c&gtm=4e6992
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtm.js?id=GTM-PJNMMGH
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.179.97 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pd-in-f97.1e100.net
Software
Google Tag Manager /
Resource Hash
8ce1e057fd8095e3d4e922d96710396c5df686cea4c532884429575e574784b7
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
private, max-age=900
content-encoding
zstd
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
expires
Sat, 12 Sep 2026 12:32:17 GMT
access-control-allow-origin
*
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
188381
date
Sat, 12 Sep 2026 12:32:17 GMT
x-xss-protection
0
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
server
Google Tag Manager
access-control-allow-headers
Cache-Control
GET
H3
200
mCsv_yLgi3c Show response
www.youtube.com/embed/ Frame 0D77
149 KB
58 KB
221ms
220ms
Document
text/html
142.251.153.4
Google LLC
General
Full URL
https://www.youtube.com/embed/mCsv_yLgi3c?start=1&feature=oembed&enablejsapi=1&origin=https%3A%2F%2Fwww.givedirectly.org
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtm.js?id=GTM-PJNMMGH
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.153.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
aeedeaed40dc6edcad6abb1e8444f5660d51467cb00b3c64aa3a9f09fb2402d6
Security Headers
Name Value
Content-Security-Policy script-src 'unsafe-eval' 'self' 'unsafe-inline' https://www.google.com https://apis.google.com https://ssl.gstatic.com https://www.gstatic.com https://www.googletagmanager.com https://www.google-analytics.com https://*.youtube.com https://*.google.com https://*.gstatic.com https://youtube.com https://www.youtube.com https://google.com https://*.doubleclick.net https://*.googleapis.com https://www.googleadservices.com https://tpc.googlesyndication.com https://www.youtubekids.com https://www.youtube-nocookie.com https://www.youtubeeducation.com https://www-onepick-opensocial.googleusercontent.com;report-uri https://csp.withgoogle.com/csp/youtube_main/allowlist require-trusted-types-for 'script' base-uri 'self';object-src 'none';script-src 'report-sample' 'nonce-TY94dNACR1iN7PfTNKt-RA' 'unsafe-inline' 'strict-dynamic' https: http: 'unsafe-eval';report-uri https://csp.withgoogle.com/csp/youtube_main/strict
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://www.givedirectly.org/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cache-control
no-cache, no-store, max-age=0, must-revalidate
content-encoding
br
content-security-policy
script-src 'unsafe-eval' 'self' 'unsafe-inline' https://www.google.com https://apis.google.com https://ssl.gstatic.com https://www.gstatic.com https://www.googletagmanager.com https://www.google-analytics.com https://*.youtube.com https://*.google.com https://*.gstatic.com https://youtube.com https://www.youtube.com https://google.com https://*.doubleclick.net https://*.googleapis.com https://www.googleadservices.com https://tpc.googlesyndication.com https://www.youtubekids.com https://www.youtube-nocookie.com https://www.youtubeeducation.com https://www-onepick-opensocial.googleusercontent.com;report-uri https://csp.withgoogle.com/csp/youtube_main/allowlist require-trusted-types-for 'script' base-uri 'self';object-src 'none';script-src 'report-sample' 'nonce-TY94dNACR1iN7PfTNKt-RA' 'unsafe-inline' 'strict-dynamic' https: http: 'unsafe-eval';report-uri https://csp.withgoogle.com/csp/youtube_main/strict
content-type
text/html; charset=utf-8
cross-origin-embedder-policy-report-only
require-corp; report-to="youtube_main"
cross-origin-opener-policy-report-only
same-origin; report-to="youtube_main"
cross-origin-resource-policy
cross-origin
date
Sat, 12 Sep 2026 12:32:17 GMT
expires
Mon, 01 Jan 1990 00:00:00 GMT
origin-trial
AmhMBR6zCLzDDxpW+HfpP67BqwIknWnyMOXOQGfzYswFmJe+fgaI6XZgAzcxOrzNtP7hEDsOo1jdjFnVr2IdxQ4AAAB4eyJvcmlnaW4iOiJodHRwczovL3lvdXR1YmUuY29tOjQ0MyIsImZlYXR1cmUiOiJXZWJWaWV3WFJlcXVlc3RlZFdpdGhEZXByZWNhdGlvbiIsImV4cGlyeSI6MTc1ODA2NzE5OSwiaXNTdWJkb21haW4iOnRydWV9 AiDEBptUfVeO93q48VdVMe/ubupazdAl8AaHP+NBzdnW8quUcHdzJUyGSfrmtpKJu7EOvwRp9ug2rEo3XU+WMAMAAAB2eyJvcmlnaW4iOiJodHRwczovL3lvdXR1YmUuY29tOjQ0MyIsImZlYXR1cmUiOiJEZXZpY2VCb3VuZFNlc3Npb25DcmVkZW50aWFsczIiLCJleHBpcnkiOjE3NzQzMTA0MDAsImlzU3ViZG9tYWluIjp0cnVlfQ==
p3p
CP="This is not a P3P policy! See http://support.google.com/accounts/answer/151657?hl=en for more info."
permissions-policy
ch-ua-arch=*, ch-ua-bitness=*, ch-ua-full-version=*, ch-ua-full-version-list=*, ch-ua-model=*, ch-ua-wow64=*, ch-ua-form-factors=*, ch-ua-platform=*, ch-ua-platform-version=*
pragma
no-cache
report-to
{"group":"youtube_main","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube_main"}]}
server
ESF
strict-transport-security
max-age=31536000
vary
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
x-content-type-options
nosniff
x-xss-protection
0
GET
H2
200
iframe_api Show response
www.youtube.com/
993 B
3 KB
397ms
217ms
Script
text/javascript
142.251.153.4
Google LLC
General
Full URL
https://www.youtube.com/iframe_api
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtm.js?id=GTM-PJNMMGH
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.153.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
309a867ab2e3ac2fa076db478f9d39b8de5e9e4d44aecd02866dc89f8f333653
Security Headers
Name Value
Content-Security-Policy script-src 'unsafe-eval' 'self' 'unsafe-inline' https://www.google.com https://apis.google.com https://ssl.gstatic.com https://www.gstatic.com https://www.googletagmanager.com https://www.google-analytics.com https://*.youtube.com https://*.google.com https://*.gstatic.com https://youtube.com https://www.youtube.com https://google.com https://*.doubleclick.net https://*.googleapis.com https://www.googleadservices.com https://tpc.googlesyndication.com https://www.youtubekids.com https://www.youtube-nocookie.com https://www.youtubeeducation.com https://www-onepick-opensocial.googleusercontent.com;report-uri https://csp.withgoogle.com/csp/youtube_main/allowlist, base-uri 'self';object-src 'none';script-src 'report-sample' 'nonce-9HFm9ooFFt6EPMQTb1dPGQ' 'unsafe-inline' 'strict-dynamic' https: http: 'unsafe-eval';report-uri https://csp.withgoogle.com/csp/youtube_main/strict, require-trusted-types-for 'script'
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
origin-trial
AmhMBR6zCLzDDxpW+HfpP67BqwIknWnyMOXOQGfzYswFmJe+fgaI6XZgAzcxOrzNtP7hEDsOo1jdjFnVr2IdxQ4AAAB4eyJvcmlnaW4iOiJodHRwczovL3lvdXR1YmUuY29tOjQ0MyIsImZlYXR1cmUiOiJXZWJWaWV3WFJlcXVlc3RlZFdpdGhEZXByZWNhdGlvbiIsImV4cGlyeSI6MTc1ODA2NzE5OSwiaXNTdWJkb21haW4iOnRydWV9, AiDEBptUfVeO93q48VdVMe/ubupazdAl8AaHP+NBzdnW8quUcHdzJUyGSfrmtpKJu7EOvwRp9ug2rEo3XU+WMAMAAAB2eyJvcmlnaW4iOiJodHRwczovL3lvdXR1YmUuY29tOjQ0MyIsImZlYXR1cmUiOiJEZXZpY2VCb3VuZFNlc3Npb25DcmVkZW50aWFsczIiLCJleHBpcnkiOjE3NzQzMTA0MDAsImlzU3ViZG9tYWluIjp0cnVlfQ==
x-content-type-options
nosniff
report-to
{"group":"youtube_main","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube_main"}]}
expires
Sat, 12 Sep 2026 12:32:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
CP="This is not a P3P policy! See http://support.google.com/accounts/answer/151657?hl=en for more info."
date
Sat, 12 Sep 2026 12:32:17 GMT
content-type
text/javascript; charset=utf-8
vary
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=31536000
content-security-policy
script-src 'unsafe-eval' 'self' 'unsafe-inline' https://www.google.com https://apis.google.com https://ssl.gstatic.com https://www.gstatic.com https://www.googletagmanager.com https://www.google-analytics.com https://*.youtube.com https://*.google.com https://*.gstatic.com https://youtube.com https://www.youtube.com https://google.com https://*.doubleclick.net https://*.googleapis.com https://www.googleadservices.com https://tpc.googlesyndication.com https://www.youtubekids.com https://www.youtube-nocookie.com https://www.youtubeeducation.com https://www-onepick-opensocial.googleusercontent.com;report-uri https://csp.withgoogle.com/csp/youtube_main/allowlist, base-uri 'self';object-src 'none';script-src 'report-sample' 'nonce-9HFm9ooFFt6EPMQTb1dPGQ' 'unsafe-inline' 'strict-dynamic' https: http: 'unsafe-eval';report-uri https://csp.withgoogle.com/csp/youtube_main/strict, require-trusted-types-for 'script'
cache-control
private, max-age=0
accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
cross-origin-resource-policy
cross-origin
permissions-policy
ch-ua-arch=*, ch-ua-bitness=*, ch-ua-full-version=*, ch-ua-full-version-list=*, ch-ua-model=*, ch-ua-wow64=*, ch-ua-form-factors=*, ch-ua-platform=*, ch-ua-platform-version=*
cross-origin-opener-policy-report-only
same-origin; report-to="youtube_main"
x-xss-protection
0
server
ESF
GET
H3
200
/ Show response
erinaceus.givedirectly.org/api/surveys/
1 KB
1 KB
143ms
143ms
Fetch
application/json
3.167.69.84
Amazon.com
General
Full URL
https://erinaceus.givedirectly.org/api/surveys/?token=phc_j1Fm3HqKiplMs7guXcEKIdcYC8CQCUOu31quq5YpXFj&_=1789216337436
Requested by
Host: erinaceus.givedirectly.org
URL: https://erinaceus.givedirectly.org/static/array.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
3.167.69.84 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-167-69-84.iad61.r.cloudfront.net
Software
envoy /
Resource Hash
e7e6649d05d4e8097557de6ae15ba06fb174da2ffdb5010788aae11b25ffcf01
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-content-type-options
nosniff
x-cache
Miss from cloudfront
x-amz-cf-id
OcEnEIMF2m3VwVxfZqp9LOch7LoTRn-USq-EjWIV88imPqLyCheijA==
date
Sat, 12 Sep 2026 12:32:17 GMT
content-type
application/json
vary
origin,Accept-Encoding
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=31536000; includeSubDomains
x-envoy-upstream-service-time
1
access-control-allow-credentials
true
referrer-policy
strict-origin-when-cross-origin
via
1.1 cf8c5b66c93d44ff2109ede7dd215622.cloudfront.net (CloudFront)
access-control-allow-origin
https://www.givedirectly.org
x-xss-protection
1; mode=block
x-amz-cf-pop
IAD61-P6
server
envoy
POST
H2
204
collect
analytics.google.com/g/
0
0
581ms
276ms
Fetch
text/plain
142.251.163.113
Google LLC
General
Full URL
https://analytics.google.com/g/collect?v=2&tid=G-GV8XF9FJ16&gtm=45je6992v870284789z8812195104za20gzb812195104zd812195104&_p=1789216336517&_gaz=1&gcd=13l3l3l3l1l1&npa=0&dma=0&_eu=AAAAAGAC&cid=1664461639.1789216338&frm=0&pscdl=noapi&rcb=8&sr=1600x1200&uaa=x86&uab=64&uafvl=Chromium%3B153.0.0.0%7CGoogle%2520Chrome%3B153.0.0.0%7CNot_A%2520Brand%3B8.0.0.0&uam=&uamb=0&uap=Linux&uapv=&uaw=0&ul=en-us&gaf=2&_s=1&tag_exp=115616985~115938465~115938468~118897920~118897930~120213116~120385423~120469145~120469153~120912438&sid=1789216337&sct=1&seg=0&dl=https%3A%2F%2Fwww.givedirectly.org%2Fliberia&dt=Cash%20Aid%20in%20Liberia%20%7C%20GiveDirectly&en=page_view&_fv=1&_nsi=1&_ss=1&gap.plf=5&tfd=7114
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtag/js?id=G-GV8XF9FJ16&cx=c&gtm=4e6992
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.163.113 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
wv-in-f113.1e100.net
Software
Golfe2 /
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, no-store, must-revalidate
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
content-security-policy-report-only
script-src 'none'; form-action 'none'; frame-src 'none'; report-uri https://csp.withgoogle.com/csp/scaffolding/ascnsrsggc:197:0
report-to
{"group":"ascnsrsggc:197:0","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/scaffolding/ascnsrsggc:197:0"}],}
expires
Fri, 01 Jan 1990 00:00:00 GMT
access-control-allow-origin
https://www.givedirectly.org
cross-origin-opener-policy-report-only
same-origin; report-to=ascnsrsggc:197:0
content-length
0
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sat, 12 Sep 2026 12:32:18 GMT
content-type
text/plain
server
Golfe2
POST
H2
204
collect
stats.g.doubleclick.net/g/
0
562 B
597ms
289ms
Ping
text/plain
192.178.155.154
Google LLC
General
Full URL
https://stats.g.doubleclick.net/g/collect?v=2&tid=G-GV8XF9FJ16&cid=1664461639.1789216338&gtm=45je6992v870284789z8812195104za20gzb812195104zd812195104&rcb=8&aip=1&dma=0&gcd=13l3l3l3l1l1&npa=0&frm=0&tag_exp=115616985~115938465~115938468~118897920~118897930~120213116~120385423~120469145~120469153~120912438
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtag/js?id=G-GV8XF9FJ16&cx=c&gtm=4e6992
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
192.178.155.154 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
yuiadrs-in-f154.1e100.net
Software
Golfe2 /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, no-store, must-revalidate
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
content-security-policy-report-only
script-src 'none'; form-action 'none'; frame-src 'none'; report-uri https://csp.withgoogle.com/csp/scaffolding/ascnsrsggc:165:0
report-to
{"group":"ascnsrsggc:165:0","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/scaffolding/ascnsrsggc:165:0"}],}
expires
Fri, 01 Jan 1990 00:00:00 GMT
access-control-allow-origin
https://www.givedirectly.org
cross-origin-opener-policy-report-only
same-origin; report-to=ascnsrsggc:165:0
content-length
0
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sat, 12 Sep 2026 12:32:18 GMT
content-type
text/plain
server
Golfe2
GET
H3
200
/ Show response
googleads.g.doubleclick.net/pagead/viewthroughconversion/10952506183/
5 KB
3 KB
261ms
137ms
Script
text/javascript
142.251.167.155
Google LLC
General
Full URL
https://googleads.g.doubleclick.net/pagead/viewthroughconversion/10952506183/?random=1789216337794&cv=11&fst=1789216337794&bg=ffffff&guid=ON&async=1&en=gtag.config&gtm=45je6992v870284789z8812195104za20gzb812195104zd812195104xec&gcd=13l3l3l3l1l1&dma=0&tag_exp=115616985~115938465~115938468~118131809~118897920~118897930~120213116~120385423~120469145~120469153~120847433~120912438&u_w=1600&u_h=1200&url=https%3A%2F%2Fwww.givedirectly.org%2Fliberia&rcb=8&frm=0&tiba=Cash%20Aid%20in%20Liberia%20%7C%20GiveDirectly&hn=www.googleadservices.com&npa=0&pscdl=noapi&auid=1823712742.1789216337&uaa=x86&uab=64&uafvl=Chromium%3B153.0.0.0%7CGoogle%2520Chrome%3B153.0.0.0%7CNot_A%2520Brand%3B8.0.0.0&uamb=0&uam=&uap=Linux&uapv=&uaw=0&data=event%3Dgtag.config&gap.plf=5&ept=9&rfmt=3&fmt=4
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtag/js?id=G-GV8XF9FJ16&cx=c&gtm=4e6992
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.167.155 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
ww-in-f155.1e100.net
Software
cafe /
Resource Hash
00ee80c3c37a18583b552a3c13e1a336a3ca6e8e24048a96a6983475b5f9a033
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, must-revalidate
timing-allow-origin
*
content-encoding
br
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
content-length
2661
date
Sat, 12 Sep 2026 12:32:18 GMT
x-xss-protection
0
content-type
text/javascript; charset=UTF-8
content-disposition
attachment; filename="f.txt"
server
cafe
POST
H3
200
/
www.google.com/rmkt/collect/10952506183/
0
0
70ms
70ms
Fetch
text/html
142.251.151.119
Google LLC
General
Full URL
https://www.google.com/rmkt/collect/10952506183/?random=1789216337794&cv=11&fst=1789216337794&fmt=8&bg=ffffff&guid=ON&async=1&en=gtag.config&gtm=45je6992v870284789z8812195104za20gzb812195104zd812195104xec&gcd=13l3l3l3l1l1&dma=0&tag_exp=115616985~115938465~115938468~118131809~118897920~118897930~120213116~120385423~120469145~120469153~120847433~120912438&u_w=1600&u_h=1200&url=https%3A%2F%2Fwww.givedirectly.org%2Fliberia&rcb=8&frm=0&tiba=Cash%20Aid%20in%20Liberia%20%7C%20GiveDirectly&hn=www.googleadservices.com&npa=0&pscdl=noapi&auid=1823712742.1789216337&uaa=x86&uab=64&uafvl=Chromium%3B153.0.0.0%7CGoogle%2520Chrome%3B153.0.0.0%7CNot_A%2520Brand%3B8.0.0.0&uamb=0&uam=&uap=Linux&uapv=&uaw=0&data=event%3Dgtag.config&gap.plf=5&ept=68&gcp=5
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtag/js?id=G-GV8XF9FJ16&cx=c&gtm=4e6992
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.151.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
/
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

POST
H3
200
collect
www.google.com/ccm/
0
0
68ms
68ms
Fetch
text/plain
142.251.151.119
Google LLC
General
Full URL
https://www.google.com/ccm/collect?rcb=8&frm=0&apvc=0&auid=1823712742.1789216337&dt=Cash%20Aid%20in%20Liberia%20%7C%20GiveDirectly&tid=AW-10952506183&en=page_view&dl=https%3A%2F%2Fwww.givedirectly.org%2Fliberia&scrsrc=www.googletagmanager.com&rnd=485911603.1789216337&navt=n&npa=0&gtm=45je6992v870284789z8812195104za20gzb812195104zd812195104xec&gcd=13l3l3l3l1l1&dma=0&tag_exp=115616985~115938465~115938468~118131809~118897920~118897930~120213116~120385423~120469145~120469153~120847433~120912438&tft=1789216337816&tfd=7137&gap.plf=5&tids=AW-10952506183&fmt=8
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtag/js?id=G-GV8XF9FJ16&cx=c&gtm=4e6992
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.151.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
/
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

GET
H2
200
www-player.css
www.youtube.com/s/player/8c3fda2d/ Frame 0D77
531 KB
0
93ms
91ms
Stylesheet
text/css
142.251.153.4
Google LLC
General
Full URL
https://www.youtube.com/s/player/8c3fda2d/www-player.css
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/mCsv_yLgi3c?start=1&feature=oembed&enablejsapi=1&origin=https%3A%2F%2Fwww.givedirectly.org
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.153.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
1e6f131e5c23998532caa01dec741cd746efdb7364cffaf33a43f227aaa0d458
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://www.youtube.com/embed/mCsv_yLgi3c?start=1&feature=oembed&enablejsapi=1&origin=https%3A%2F%2Fwww.givedirectly.org

Response headers

content-encoding
br
age
25285
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Sun, 12 Sep 2027 05:30:52 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sat, 12 Sep 2026 05:30:52 GMT
last-modified
Mon, 07 Sep 2026 04:37:27 GMT
content-type
text/css
vary
Accept-Encoding, Origin
cache-control
public, max-age=31536000
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
58390
x-xss-protection
0
server
sffe
GET
H2
200
m=root,base
www.youtube.com/s/_/ytembeds/_/ss/k=ytembeds.base.HY7wD9GGp-g.L.W.O/am=AAAAQA/d=1/br=1/rs=AGKMywE4Kjs9hFDhD74lwcLYIXdA_OMvQQ/ Frame 0D77
0
0
140ms
139ms
Stylesheet
text/css
142.251.153.4
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/ss/k=ytembeds.base.HY7wD9GGp-g.L.W.O/am=AAAAQA/d=1/br=1/rs=AGKMywE4Kjs9hFDhD74lwcLYIXdA_OMvQQ/m=root,base
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/mCsv_yLgi3c?start=1&feature=oembed&enablejsapi=1&origin=https%3A%2F%2Fwww.givedirectly.org
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.153.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://www.youtube.com/embed/mCsv_yLgi3c?start=1&feature=oembed&enablejsapi=1&origin=https%3A%2F%2Fwww.givedirectly.org

Response headers

age
84965
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Sat, 11 Sep 2027 12:56:12 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 11 Sep 2026 12:56:12 GMT
last-modified
Fri, 11 Sep 2026 03:12:40 GMT
content-type
text/css; charset=UTF-8
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
0
x-xss-protection
0
server
sffe
GET
H3
200
m=root,base Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywHdVJjs6ktwWXG8Pg3CpN4ZEVjBaQ/ Frame 0D77
456 KB
155 KB
61ms
60ms
Script
text/javascript
142.251.153.4
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywHdVJjs6ktwWXG8Pg3CpN4ZEVjBaQ/m=root,base
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/mCsv_yLgi3c?start=1&feature=oembed&enablejsapi=1&origin=https%3A%2F%2Fwww.givedirectly.org
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.153.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
555e95e5af65cfd867790ac83d0f93780e6a63078135648b21c4fb935c1e04b0
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/mCsv_yLgi3c?start=1&feature=oembed&enablejsapi=1&origin=https%3A%2F%2Fwww.givedirectly.org
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
84970
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Sat, 11 Sep 2027 12:56:07 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 11 Sep 2026 12:56:07 GMT
last-modified
Fri, 11 Sep 2026 09:12:02 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
158737
x-xss-protection
0
server
sffe
GET
H3
200
base.js Show response
www.youtube.com/s/player/8c3fda2d/player_embed_es6.vflset/en_US/ Frame 0D77
2 MB
0
0ms
0ms
Script
text/javascript
142.251.153.4
Google LLC
General
Full URL
https://www.youtube.com/s/player/8c3fda2d/player_embed_es6.vflset/en_US/base.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/mCsv_yLgi3c?start=1&feature=oembed&enablejsapi=1&origin=https%3A%2F%2Fwww.givedirectly.org
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.153.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
9d66ed39cd90111abe8be07798b65f01076983dcead837eada3c68219e1cd383
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/mCsv_yLgi3c?start=1&feature=oembed&enablejsapi=1&origin=https%3A%2F%2Fwww.givedirectly.org
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
111207
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Sat, 11 Sep 2027 05:38:50 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 11 Sep 2026 05:38:50 GMT
last-modified
Mon, 07 Sep 2026 04:37:27 GMT
content-type
text/javascript
vary
Accept-Encoding, Origin
cache-control
public, max-age=31536000
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
483559
x-xss-protection
0
server
sffe
GET
H3
200
KFO7CnqEu92Fr1ME7kSn66aGLdTylUAMa3yUBA.woff2
fonts.gstatic.com/s/roboto/v48/ Frame 0D77
39 KB
0
252ms
121ms
Font
font/woff2
142.250.31.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/roboto/v48/KFO7CnqEu92Fr1ME7kSn66aGLdTylUAMa3yUBA.woff2
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/mCsv_yLgi3c?start=1&feature=oembed&enablejsapi=1&origin=https%3A%2F%2Fwww.givedirectly.org
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.250.31.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bj-in-f94.1e100.net
Software
sffe /
Resource Hash
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://www.youtube.com
Referer
https://www.youtube.com/

Response headers

age
3994
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Sun, 12 Sep 2027 11:25:43 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sat, 12 Sep 2026 11:25:43 GMT
last-modified
Thu, 29 May 2025 23:30:55 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
40128
x-xss-protection
0
server
sffe
GET
H3
200
www-widgetapi.js Show response
www.youtube.com/s/player/8c3fda2d/www-widgetapi.vflset/
26 KB
9 KB
60ms
60ms
Script
text/javascript
142.251.151.119
Google LLC
General
Full URL
https://www.youtube.com/s/player/8c3fda2d/www-widgetapi.vflset/www-widgetapi.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/iframe_api
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.151.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
c2dcf46501a48a87a7859596834012e81569a181f7b80bda4d91b04798f84751
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
9816
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Sun, 12 Sep 2027 09:48:41 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sat, 12 Sep 2026 09:48:41 GMT
last-modified
Mon, 07 Sep 2026 04:37:27 GMT
content-type
text/javascript
vary
Accept-Encoding, Origin
cache-control
public, max-age=31536000
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
8877
x-xss-protection
0
server
sffe
GET
H3
200
1507191883453125 Show response
connect.facebook.net/signals/config/
327 KB
80 KB
188ms
187ms
Script
application/x-javascript
57.144.70.128
Facebook
General
Full URL
https://connect.facebook.net/signals/config/1507191883453125?v=2.9.398&r=stable&domain=www.givedirectly.org&hme=457e068698591ac437afb4b2e5fbe0266b08712615b8792436a91385ebda0da3&ex_m=115%2C227%2C166%2C26%2C80%2C81%2C158%2C76%2C75%2C11%2C176%2C100%2C20%2C150%2C138%2C45%2C83%2C88%2C146%2C171%2C178%2C31%2C17%2C30%2C18%2C32%2C33%2C34%2C36%2C54%2C159%2C85%2C123%2C22%2C24%2C50%2C46%2C48%2C47%2C93%2C102%2C106%2C121%2C157%2C160%2C52%2C122%2C28%2C25%2C130%2C77%2C42%2C162%2C161%2C163%2C154%2C152%2C29%2C41%2C65%2C120%2C173%2C78%2C21%2C125%2C91%2C74%2C23%2C95%2C96%2C127%2C94%2C148%2C147%2C151%2C107%2C172%2C175%2C40%2C55%2C124%2C53%2C8%2C4%2C5%2C7%2C6%2C3%2C101%2C112%2C180%2C179%2C194%2C241%2C82%2C255%2C254%2C253%2C14%2C27%2C39%2C61%2C114%2C67%2C10%2C71%2C108%2C109%2C110%2C116%2C141%2C37%2C35%2C143%2C144%2C145%2C140%2C139%2C167%2C84%2C170%2C168%2C169%2C56%2C66%2C134%2C19%2C174%2C51%2C305%2C306%2C307%2C304%2C320%2C344%2C234%2C223%2C68%2C224%2C222%2C347%2C338%2C58%2C235%2C118%2C142%2C90%2C132%2C60%2C131%2C137%2C136%2C64%2C72%2C70%2C164%2C86%2C87%2C126%2C43%2C38%2C59%2C62%2C111%2C177%2C1%2C135%2C16%2C133%2C12%2C2%2C63%2C103%2C15%2C73%2C69%2C129%2C99%2C98%2C182%2C183%2C104%2C105%2C9%2C113%2C181%2C57%2C155%2C97%2C89%2C79%2C128%2C117%2C49%2C156%2C0%2C92%2C149%2C153%2C165%2C44%2C119%2C13%2C184
Requested by
Host: connect.facebook.net
URL: https://connect.facebook.net/en_US/fbevents.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
57.144.70.128 Reston, United States, ASN32934 (FACEBOOK - Facebook, Inc., US),
Reverse DNS
xx-fbcdn-shv-01-xxc1.fbcdn.net
Software
/
Resource Hash
bad45c3fb085c6b8a5840059d3a5abbe0205a9e44ac0fb5153a82b1030e0dfe0
Security Headers
Name Value
Content-Security-Policy default-src *.facebook.com *.fbcdn.net *.facebook.net 'self' blob:;script-src *.facebook.com *.fbcdn.net *.facebook.net blob: 'self' 'nonce-a9fg5E6j';style-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob: 'unsafe-inline';connect-src *.facebook.com facebook.com *.fbcdn.net *.facebook.net wss://*.facebook.com:* wss://*.fbcdn.net attachment.fbsbx.com *.cdninstagram.com blob: 'self' data: https://edge-chat.facebook.net https://edge-chat-latest.facebook.net wss://edge-chat-latest.facebook.net wss://edge-chat.facebook.net wss://edge-chat.socialplugin.facebook.net wss://edge-chat-latest.socialplugin.facebook.net https://edge-chat.socialplugin.facebook.net https://edge-chat-latest.socialplugin.facebook.net;font-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;img-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;media-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;child-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;frame-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;manifest-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;object-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;worker-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;block-all-mixed-content;upgrade-insecure-requests;report-uri https://www.facebook.com/csp/reporting/?m=c&minimize=0;
Strict-Transport-Security max-age=31536000; preload; includeSubDomains
X-Content-Type-Options nosniff
X-Frame-Options DENY
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
report-to
{"max_age":2592000,"endpoints":[{"url":"https:\/\/www.facebook.com\/browser_reporting\/coop\/?minimize=0"}],"group":"coop_report","include_subdomains":true}, {"max_age":86400,"endpoints":[{"url":"https:\/\/www.facebook.com\/browser_reporting\/coep\/?minimize=0"}],"group":"coep_report"}, {"max_age":21600,"endpoints":[{"url":"https:\/\/www.facebook.com\/ajax\/browser_error_reports\/"}],"group":"permissions_policy"}
x-content-type-options
nosniff
expires
Sat, 01 Jan 2000 00:00:00 GMT
alt-svc
h3=":443"; ma=86400
date
Sat, 12 Sep 2026 12:32:18 GMT
content-type
application/x-javascript; charset=utf-8
vary
Accept-Encoding
cross-origin-embedder-policy-report-only
require-corp;report-to="coep_report"
priority
u=3,i
x-frame-options
DENY
strict-transport-security
max-age=31536000; preload; includeSubDomains
reporting-endpoints
coop_report="https://www.facebook.com/browser_reporting/coop/?minimize=0", coep_report="https://www.facebook.com/browser_reporting/coep/?minimize=0", permissions_policy="https://www.facebook.com/ajax/browser_error_reports/"
content-security-policy
default-src *.facebook.com *.fbcdn.net *.facebook.net 'self' blob:;script-src *.facebook.com *.fbcdn.net *.facebook.net blob: 'self' 'nonce-a9fg5E6j';style-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob: 'unsafe-inline';connect-src *.facebook.com facebook.com *.fbcdn.net *.facebook.net wss://*.facebook.com:* wss://*.fbcdn.net attachment.fbsbx.com *.cdninstagram.com blob: 'self' data: https://edge-chat.facebook.net https://edge-chat-latest.facebook.net wss://edge-chat-latest.facebook.net wss://edge-chat.facebook.net wss://edge-chat.socialplugin.facebook.net wss://edge-chat-latest.socialplugin.facebook.net https://edge-chat.socialplugin.facebook.net https://edge-chat-latest.socialplugin.facebook.net;font-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;img-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;media-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;child-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;frame-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;manifest-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;object-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;worker-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;block-all-mixed-content;upgrade-insecure-requests;report-uri https://www.facebook.com/csp/reporting/?m=c&minimize=0;
cache-control
public, max-age=1200
timing-allow-origin
*
cross-origin-opener-policy
same-origin-allow-popups
x-fb-connection-quality
GOOD; q=0.7, rtt=117, rtx=0, c=118, mss=1232, tbw=124252, tp=112, tpl=0, uplat=68, ullat=0
pragma
public
x-fb-debug
fzKMi7UtHKZtRS3e1sfrxvIQC2OpTB2OmCYS3w+9Ojp4GlATTz7AmU+jYXNUVWNF5WXKn1z6R9btDgNqp1QKpA==
cross-origin-resource-policy
cross-origin
permissions-policy
accelerometer=(), attribution-reporting=(), autoplay=(), bluetooth=(), camera=(), ch-device-memory=(), ch-downlink=(), ch-dpr=(), ch-ect=(), ch-rtt=(), ch-save-data=(), ch-ua-arch=(), ch-ua-bitness=(), ch-viewport-height=(), ch-viewport-width=(), ch-width=(), clipboard-read=(), clipboard-write=(), compute-pressure=(), display-capture=(), encrypted-media=(), fullscreen=(self), gamepad=(), geolocation=(), gyroscope=(), hid=(), idle-detection=(), interest-cohort=(), keyboard-map=(), local-fonts=(), magnetometer=(), microphone=(), midi=(), otp-credentials=(), payment=(), picture-in-picture=(), private-state-token-issuance=(), publickey-credentials-get=(), screen-wake-lock=(), serial=(), shared-storage=(), shared-storage-select-url=(), private-state-token-redemption=(), usb=(), unload=(self), window-management=(), xr-spatial-tracking=();report-to="permissions_policy"
document-policy
force-load-at-top, include-js-call-stacks-in-crash-reports
x-xss-protection
0
origin-agent-cluster
?1
GET
H3
200
id Show response
googleads.g.doubleclick.net/pagead/ Frame 0D77
Redirect Chain
  • https://googleads.g.doubleclick.net/pagead/id
  • https://googleads.g.doubleclick.net/pagead/id?slf_rd=1
100 B
146 B
131ms
130ms
XHR
application/json
142.251.167.157
Google LLC
General
Full URL
https://googleads.g.doubleclick.net/pagead/id?slf_rd=1
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/mCsv_yLgi3c?start=1&feature=oembed&enablejsapi=1&origin=https%3A%2F%2Fwww.givedirectly.org
Protocol
H3
Server
142.251.167.157 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
ww-in-f157.1e100.net
Software
cafe /
Resource Hash
9239979ee19c4362f6fbb3be5c4f02b04b17f25272ba02b490d9ff904aa446f9
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer
https://www.youtube.com/

Response headers

content-encoding
gzip
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
date
Sat, 12 Sep 2026 12:32:18 GMT
content-type
application/json; charset=UTF-8
content-disposition
attachment; filename="f.txt"
cache-control
no-cache, no-store, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
access-control-allow-origin
https://www.youtube.com
content-length
120
x-xss-protection
0
server
cafe

Redirect headers

x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
date
Sat, 12 Sep 2026 12:32:18 GMT
content-type
text/html; charset=UTF-8
cache-control
no-cache, no-store, must-revalidate
location
https://googleads.g.doubleclick.net/pagead/id?slf_rd=1
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
access-control-allow-origin
https://www.youtube.com
content-length
0
x-xss-protection
0
server
cafe
GET
H2
200
ad_status.js Show response
static.doubleclick.net/instream/ Frame 0D77
29 B
495 B
506ms
185ms
Script
text/javascript
172.253.139.148
Google LLC
General
Full URL
https://static.doubleclick.net/instream/ad_status.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywHdVJjs6ktwWXG8Pg3CpN4ZEVjBaQ/m=root,base
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.253.139.148 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
yuiadsk-in-f148.1e100.net
Software
sffe /
Resource Hash
eed0dc1fdb5d97ed188ae16fd5e1024a5bb744af47340346be2146300a6c54b9
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

age
570
report-to
{"group":"ads-doubleclick-media","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/ads-doubleclick-media"}]}
x-content-type-options
nosniff
expires
Sat, 12 Sep 2026 12:37:48 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sat, 12 Sep 2026 12:22:48 GMT
last-modified
Thu, 12 Dec 2013 23:40:16 GMT
content-type
text/javascript
cache-control
public, max-age=900
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to="ads-doubleclick-media"
content-length
29
x-xss-protection
0
server
sffe
GET
H3
200
m=r78Drb Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/ck=ytembeds.base.HY7wD9GGp-g.L.W.O/am=AAAAQA/d=1/exm=base,root/excm=base,root/ed=1/br=1/rs=AGKMywEii8DElVVeiaz1NP5LoXHZcDQ... Frame 0D77
906 KB
219 KB
66ms
65ms
Script
text/javascript
142.251.153.4
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/ck=ytembeds.base.HY7wD9GGp-g.L.W.O/am=AAAAQA/d=1/exm=base,root/excm=base,root/ed=1/br=1/rs=AGKMywEii8DElVVeiaz1NP5LoXHZcDQCWg/m=r78Drb
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywHdVJjs6ktwWXG8Pg3CpN4ZEVjBaQ/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.153.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
86b742cfa596799c1a5856ba629afdd7b7b1e5478112bbb2101d126b9a2c75d9
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/mCsv_yLgi3c?start=1&feature=oembed&enablejsapi=1&origin=https%3A%2F%2Fwww.givedirectly.org
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
84964
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Sat, 11 Sep 2027 12:56:14 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 11 Sep 2026 12:56:14 GMT
last-modified
Fri, 11 Sep 2026 03:12:40 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
223971
x-xss-protection
0
server
sffe
GET
H3
200
oTewMYiCjXRyFyoMElq9QP7iZHeOrHddy9i1KLC2L6Y.js Show response
www.google.com/js/th/ Frame 0D77
62 KB
24 KB
129ms
60ms
Script
text/javascript
142.251.157.119
Google LLC
General
Full URL
https://www.google.com/js/th/oTewMYiCjXRyFyoMElq9QP7iZHeOrHddy9i1KLC2L6Y.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywHdVJjs6ktwWXG8Pg3CpN4ZEVjBaQ/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.157.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
a137b03188828d7472172a0c125abd40fee264778eac775dcbd8b528b0b62fa6
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
111499
report-to
{"group":"botguard-scs","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/botguard-scs"}]}
x-content-type-options
nosniff
expires
Sat, 11 Sep 2027 05:33:59 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 11 Sep 2026 05:33:59 GMT
last-modified
Mon, 31 Aug 2026 16:00:00 GMT
content-type
text/javascript
vary
Accept-Encoding
cache-control
public, max-age=31536000
cross-origin-opener-policy
same-origin; report-to="botguard-scs"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/botguard-scs
accept-ranges
bytes
content-length
24543
x-xss-protection
0
server
sffe
GET
H2
200
10203833.json Show response
s.yimg.com/wi/config/
2 B
200 B
606ms
288ms
XHR
application/json
69.147.92.11
Yahoo Holdings Inc.
General
Full URL
https://s.yimg.com/wi/config/10203833.json
Requested by
Host: s.yimg.com
URL: https://s.yimg.com/wi/ytc.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
69.147.92.11 Ashburn, United States, ASN14777 (YAHOO - Yahoo Holdings Inc., US),
Reverse DNS
e1.ycpi.vip.dca.yahoo.com
Software
ATS /
Resource Hash
44136fa355b3678a1146ad16f7e8649e94fb4fc21fe77e8310c060f61caaff8a
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
cache-control
public,max-age=3600
age
1112
ats-carp-promotion
1
x-content-type-options
nosniff
referrer-policy
no-referrer-when-downgrade
access-control-allow-origin
*
content-length
2
date
Sat, 12 Sep 2026 12:13:46 GMT
content-type
application/json
vary
Accept-Encoding,Origin
server
ATS
GET
H2
200
insight.old.min.js Show response
snap.licdn.com/li.lms-analytics/
52 KB
19 KB
147ms
140ms
Script
application/javascript
23.55.176.231
AKAMAI-ASN1 Akama...
General
Full URL
https://snap.licdn.com/li.lms-analytics/insight.old.min.js
Requested by
Host: snap.licdn.com
URL: https://snap.licdn.com/li.lms-analytics/insight.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
23.55.176.231 Ashburn, United States, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a23-55-176-231.deploy.static.akamaitechnologies.com
Software
/
Resource Hash
246646a9adecc53ddd648f6073306ccb3ad17e926d9ef5ccfffd6975c092feb5
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=86400
content-encoding
gzip
x-cdn-proto
HTTP2
x-cdn
AKAM
x-content-type-options
nosniff
accept-ranges
bytes
access-control-allow-origin
*
content-length
18894
date
Sat, 12 Sep 2026 12:32:18 GMT
last-modified
Sun, 17 May 2026 09:47:35 GMT
content-type
application/javascript;charset=utf-8
vary
Accept-Encoding
x-amz-server-side-encryption
AES256
GET
H3
200
/
www.google.com/pagead/1p-user-list/10952506183/
42 B
64 B
77ms
77ms
Image
image/gif
142.251.151.119
Google LLC
General
Full URL
https://www.google.com/pagead/1p-user-list/10952506183/?random=1789216337794&cv=11&fst=1789214400000&bg=ffffff&guid=ON&async=1&en=gtag.config&gtm=45je6992v870284789z8812195104za20gzb812195104zd812195104xec&gcd=13l3l3l3l1l1&dma=0&tag_exp=115616985~115938465~115938468~118131809~118897920~118897930~120213116~120385423~120469145~120469153~120847433~120912438&u_w=1600&u_h=1200&url=https%3A%2F%2Fwww.givedirectly.org%2Fliberia&rcb=8&frm=0&tiba=Cash%20Aid%20in%20Liberia%20%7C%20GiveDirectly&hn=www.googleadservices.com&npa=0&pscdl=noapi&auid=1823712742.1789216337&uaa=x86&uab=64&uafvl=Chromium%3B153.0.0.0%7CGoogle%2520Chrome%3B153.0.0.0%7CNot_A%2520Brand%3B8.0.0.0&uamb=0&uam=&uap=Linux&uapv=&uaw=0&data=event%3Dgtag.config&gap.plf=5&ept=9&rfmt=3&fmt=3&is_vtc=1&cid=CAQS1AEAQM4h3OmVKsfJLqyfsVAi1dNJDn0Pt8pGiYmPmkNekoiQgAwArfDzqRTvNbuhJJ-O4ByYxJJ537dO9xE1nfbKyw4V3inUIJQGx6znr_ecV76jecAaGhIr_-dika0YpgqZRoOVkn4V6X_3Az46T-RWiuITYkkBNBom3c9uaUuE6hkLDqcxYMMLEhs18qWcKMjYgtFO3qZ76OR5Jlb8p1Id5fpR_KyMNrFxt3w9CJkaWhIFqlZxyvdnADwaLJgqF8IjDEQ1SeFxDREdtXUigmyXvZFylA&random=4291258850&rmt_tld=0&ipr=y
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.151.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
cafe /
Resource Hash
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
Security Headers
Name Value
Content-Security-Policy script-src 'none'; object-src 'none'
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-security-policy
script-src 'none'; object-src 'none'
cache-control
no-cache, no-store, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
42
date
Sat, 12 Sep 2026 12:32:18 GMT
x-xss-protection
0
content-type
image/gif
server
cafe
GET
H3
200
/
www.facebook.com/tr/
0
20 B
261ms
128ms
Image
text/plain
57.144.70.1
Facebook
General
Full URL
https://www.facebook.com/tr/?id=1507191883453125&ev=PageView&dl=https%3A%2F%2Fwww.givedirectly.org%2Fliberia&rl=&if=false&ts=1789216338229&iw=false&sw=1600&sh=1200&v=2.9.398&r=stable&ec=0&o=12318&aems=0%3B0&fbp=fb.1.1789216338219.92955045817569586&ler=empty&cdl=API_unavailable&pmd[title]=Cash%20Aid%20in%20Liberia%20%7C%20GiveDirectly&pmd[locale]=en_US&pmd[description]=Help%20deliver%20cash%20to%20the%20poorest%20and%20most%20remote%20communities%20in%20Liberia.&plt=6020.100002288818&iss=1&imft=1&tz=-600&it=1789216337972&coo=false&expv2[0]=pl0&expv2[1]=el2&expv2[2]=bc1&expv2[3]=ra2&expv2[4]=rp2&expv2[5]=ct3&expv2[6]=hf0&expv2[7]=sd1&expv2[8]=sp1&expv2[9]=ek1&expv2[10]=pc1&expv2[11]=gs1&expv2[12]=zs1&expv2[13]=cp1&expv2[14]=es1&expv2[15]=ac1&expv2[16]=so1&expv2[17]=wc3&expv2[18]=la1&expv2[19]=sf1&expv2[20]=da1&expv2[21]=io1&expv2[22]=ae1&expv2[23]=sx1&expv2[24]=if1&expv2[25]=fd1&expv2[26]=bg3&expv2[27]=mg3&expv2[28]=kl3&expv2[29]=sg3&expv2[30]=mk3&expv2[31]=sn3&expv2[32]=ec3&expv2[33]=mp3&expv2[34]=ps3&expv2[35]=fx3&expv2[36]=vt3&expv2[37]=dp1&expv2[38]=fw1&expv2[39]=cn1&expv2[40]=tz1&expv2[41]=pe1&expv2[42]=ee1&expv2[43]=bu1&expv2[44]=ta1&expv2[45]=ot0&rqm=GET
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
57.144.70.1 Reston, United States, ASN32934 (FACEBOOK - Facebook, Inc., US),
Reverse DNS
edge-star-mini-shv-01-xxc1.facebook.com
Software
proxygen-bolt /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
x-fb-connection-quality
GOOD; q=0.7, rtt=127, rtx=0, c=24, mss=1232, tbw=8780, tp=13, tpl=0, uplat=0, ullat=0
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
access-control-allow-origin
alt-svc
h3=":443"; ma=86400
content-length
0
date
Sat, 12 Sep 2026 12:32:18 GMT
content-type
text/plain
server
proxygen-bolt
priority
u=1,i
GET
H3
200
m=cwx9N Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/ck=ytembeds.base.HY7wD9GGp-g.L.W.O/am=AAAAQA/d=1/exm=base,r78Drb,root/excm=base,root/ed=1/br=1/rs=AGKMywEii8DElVVeiaz1NP5L... Frame 0D77
66 KB
17 KB
60ms
60ms
Script
text/javascript
142.251.157.119
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/ck=ytembeds.base.HY7wD9GGp-g.L.W.O/am=AAAAQA/d=1/exm=base,r78Drb,root/excm=base,root/ed=1/br=1/rs=AGKMywEii8DElVVeiaz1NP5LoXHZcDQCWg/m=cwx9N
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywHdVJjs6ktwWXG8Pg3CpN4ZEVjBaQ/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.157.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
9a6f174d593d8404d55c3ba5b8ddc199d63196b87c1cf40b061fe0266660af3d
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/mCsv_yLgi3c?start=1&feature=oembed&enablejsapi=1&origin=https%3A%2F%2Fwww.givedirectly.org
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
84964
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Sat, 11 Sep 2027 12:56:14 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 11 Sep 2026 12:56:14 GMT
last-modified
Fri, 11 Sep 2026 03:12:40 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
17678
x-xss-protection
0
server
sffe
GET
H2
200
sddefault.jpg
i.ytimg.com/vi/mCsv_yLgi3c/ Frame 0D77
55 KB
55 KB
393ms
128ms
Image
image/jpeg
172.253.62.119
Google LLC
General
Full URL
https://i.ytimg.com/vi/mCsv_yLgi3c/sddefault.jpg
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/mCsv_yLgi3c?start=1&feature=oembed&enablejsapi=1&origin=https%3A%2F%2Fwww.givedirectly.org
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.253.62.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bc-in-f119.1e100.net
Software
sffe /
Resource Hash
95682117b2f72a2b381c725cbbf2fb87404b954781c2c32764595eab7fb6af89
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

etag
"1692127475"
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Sat, 12 Sep 2026 14:32:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sat, 12 Sep 2026 12:32:18 GMT
content-type
image/jpeg
cache-control
public, max-age=7200
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
56061
x-xss-protection
0
server
sffe
GET
H3
200
collect
px.ads.linkedin.com/
Redirect Chain
  • https://px.ads.linkedin.com/collect?v=2&fmt=js&pid=5456490&time=1789216338378&li_adsId=09d7f9f8-2b51-43e4-a029-8a71ed0e2e49&url=https%3A%2F%2Fwww.givedirectly.org%2Fliberia
  • https://px.ads.linkedin.com/collect?v=2&fmt=js&pid=5456490&time=1789216338378&li_adsId=09d7f9f8-2b51-43e4-a029-8a71ed0e2e49&url=https%3A%2F%2Fwww.givedirectly.org%2Fliberia&cookiesTest=true
  • https://www.linkedin.com/px/li_sync?redirect=https%3A%2F%2Fpx.ads.linkedin.com%2Fcollect%3Fv%3D2%26fmt%3Djs%26pid%3D5456490%26time%3D1789216338378%26li_adsId%3D09d7f9f8-2b51-43e4-a029-8a71ed0e2e49%...
  • https://px.ads.linkedin.com/collect?v=2&fmt=js&pid=5456490&time=1789216338378&li_adsId=09d7f9f8-2b51-43e4-a029-8a71ed0e2e49&url=https%3A%2F%2Fwww.givedirectly.org%2Fliberia&cookiesTest=true&liSync=...
0
492 B
120ms
120ms
Image
application/javascript
104.18.41.41
Cloudflare
General
Full URL
https://px.ads.linkedin.com/collect?v=2&fmt=js&pid=5456490&time=1789216338378&li_adsId=09d7f9f8-2b51-43e4-a029-8a71ed0e2e49&url=https%3A%2F%2Fwww.givedirectly.org%2Fliberia&cookiesTest=true&liSync=true
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H3
Server
104.18.41.41 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer
https://www.givedirectly.org/

Response headers

linkedin-action
1
cf-cache-status
DYNAMIC
x-li-fabric
prod-lor1
x-content-type-options
nosniff
x-li-proto
http/3
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Sat, 12 Sep 2026 12:32:18 GMT
content-type
application/javascript
priority
u=3,i
x-li-pop
cf-prod-lor1-x
strict-transport-security
max-age=31536000
cf-ray
a39eef262c9af7b9-LAX
x-li-uuid
AAZbSGRO18clNZF54oC1Pw==
content-length
0
server
cloudflare

Redirect headers

linkedin-action
1
cf-cache-status
DYNAMIC
x-li-fabric
prod-lor1
x-content-type-options
nosniff
expires
Thu, 01 Jan 1970 00:00:00 GMT
x-li-proto
http/2
alt-svc
h3=":443"; ma=86400
date
Sat, 12 Sep 2026 12:32:18 GMT
x-frame-options
sameorigin
strict-transport-security
max-age=31536000
x-li-pop
cf-prod-lor1-x
content-security-policy
frame-ancestors 'self'
cache-control
no-cache, no-store, no-transform
location
https://px.ads.linkedin.com/collect?v=2&fmt=js&pid=5456490&time=1789216338378&li_adsId=09d7f9f8-2b51-43e4-a029-8a71ed0e2e49&url=https%3A%2F%2Fwww.givedirectly.org%2Fliberia&cookiesTest=true&liSync=true
pragma
no-cache
cf-ray
a39eef2578d73478-LAX
x-li-uuid
AAZbSGRNLX1OoNis8oAm9Q==
content-length
0
server
cloudflare
GET
H2
200
AIdro_l3A7qNgdsCS4lscxDMII0OPsSpH-5EdZR_-prGXDRHEA=s68-c-k-c0x00ffffff-no-rj
yt3.ggpht.com/ytc/ Frame 0D77
2 KB
2 KB
604ms
298ms
Image
image/jpeg
192.178.155.132
Google LLC
General
Full URL
https://yt3.ggpht.com/ytc/AIdro_l3A7qNgdsCS4lscxDMII0OPsSpH-5EdZR_-prGXDRHEA=s68-c-k-c0x00ffffff-no-rj
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/mCsv_yLgi3c?start=1&feature=oembed&enablejsapi=1&origin=https%3A%2F%2Fwww.givedirectly.org
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
192.178.155.132 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
yuiadrs-in-f132.1e100.net
Software
fife /
Resource Hash
f43939258cf629ebe3373bba92cce6cd86f5d8aab6e5cfe52ca161ad831622ac
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

access-control-expose-headers
Content-Length
etag
"v175"
x-content-type-options
nosniff
expires
Sun, 13 Sep 2026 12:32:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sat, 12 Sep 2026 12:32:18 GMT
content-type
image/jpeg
vary
Origin
content-disposition
inline;filename="unnamed.jpg"
cache-control
public, max-age=86400, no-transform
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
content-length
1943
x-xss-protection
0
server
fife
GET
H2
200
67px.svg Show response
www.gstatic.com/youtube/img/icons/mweb/youtube_fill/logo/v2/ Frame 0D77
478 B
727 B
531ms
285ms
Fetch
image/svg+xml
192.179.24.94
Google LLC
General
Full URL
https://www.gstatic.com/youtube/img/icons/mweb/youtube_fill/logo/v2/67px.svg
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/ck=ytembeds.base.HY7wD9GGp-g.L.W.O/am=AAAAQA/d=1/exm=base,root/excm=base,root/ed=1/br=1/rs=AGKMywEii8DElVVeiaz1NP5LoXHZcDQCWg/m=r78Drb
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
192.179.24.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
rz-in-f94.1e100.net
Software
sffe /
Resource Hash
6fa88a20839537ae66da730e5bd183035265176d972bc8df075b89da0c6186ea
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
266444
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Thu, 09 Sep 2027 10:31:34 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 09 Sep 2026 10:31:34 GMT
last-modified
Wed, 06 Sep 2023 03:18:00 GMT
content-type
image/svg+xml
vary
Accept-Encoding, Origin
cache-control
public, max-age=31536000
cross-origin-opener-policy
same-origin; report-to="youtube"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
https://www.youtube.com
content-length
272
x-xss-protection
0
server
sffe
GET
H3
204
generate_204
www.youtube.com/ Frame 0D77
0
10 B
60ms
59ms
Image
text/plain
142.251.157.119
Google LLC
General
Full URL
https://www.youtube.com/generate_204?xiYMbg
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/mCsv_yLgi3c?start=1&feature=oembed&enablejsapi=1&origin=https%3A%2F%2Fwww.givedirectly.org
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.157.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/mCsv_yLgi3c?start=1&feature=oembed&enablejsapi=1&origin=https%3A%2F%2Fwww.givedirectly.org
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
0
date
Sat, 12 Sep 2026 12:32:18 GMT
cross-origin-resource-policy
cross-origin
OPTIONS
H2
200
GenerateIT
jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/ Frame
0
0
282ms
119ms
Preflight
text/html
172.217.114.4
Google LLC
General
Full URL
https://jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/GenerateIT
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
172.217.114.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

Accept
*/*
Access-Control-Request-Headers
content-type,x-goog-api-key
Access-Control-Request-Method
POST
Origin
https://www.youtube.com
Sec-Fetch-Mode
cors
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36

Response headers

access-control-allow-credentials
true
access-control-allow-headers
content-type,x-goog-api-key
access-control-allow-methods
DELETE,GET,HEAD,OPTIONS,PATCH,POST,PUT
access-control-allow-origin
https://www.youtube.com
access-control-max-age
3600
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
0
content-type
text/html
date
Sat, 12 Sep 2026 12:32:18 GMT
server
ESF
vary
origin referer x-origin
x-content-type-options
nosniff
x-frame-options
SAMEORIGIN
x-xss-protection
0
POST
H2
200
GenerateIT Show response
jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/ Frame 0D77
94 B
304 B
74ms
71ms
XHR
application/json+protobuf
172.217.114.4
Google LLC
General
Full URL
https://jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/GenerateIT
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywHdVJjs6ktwWXG8Pg3CpN4ZEVjBaQ/m=root,base
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
172.217.114.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
2976fbc22a5a7339d5278e01608d61c4f56a5d20165cafb51ae25d7802bb96f6
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

X-Goog-Api-Key
AIzaSyDyT5W0Jh49F30Pqqtyfdf7pDLFKLJoAnw
sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
application/json+protobuf
sec-ch-ua-mobile
?0

Response headers

access-control-expose-headers
vary,vary,vary,content-encoding,date,server,content-length
content-encoding
gzip
access-control-allow-credentials
true
x-content-type-options
nosniff
access-control-allow-origin
https://www.youtube.com
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
114
date
Sat, 12 Sep 2026 12:32:18 GMT
x-xss-protection
0
content-type
application/json+protobuf; charset=UTF-8
vary
Origin, X-Origin, Referer
server
ESF
x-frame-options
SAMEORIGIN
GET
H2
200
sp.pl
sp.analytics.yahoo.com/
43 B
677 B
483ms
215ms
Image
image/gif
54.160.143.175
Amazon.com
General
Full URL
https://sp.analytics.yahoo.com/sp.pl?a=10000&d=Sat%2C%2012%20Sep%202026%2012%3A32%3A18%20GMT&n=10&b=Cash%20Aid%20in%20Liberia%20%7C%20GiveDirectly&.yp=10203833&f=https%3A%2F%2Fwww.givedirectly.org%2Fliberia&enc=UTF-8&yv=1.17.1&tagmgr=gtm
Requested by
Host: www.givedirectly.org
URL: https://www.givedirectly.org/liberia
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
54.160.143.175 Ashburn, United States, ASN14618 (AMAZON-AES - Amazon.com, Inc., US),
Reverse DNS
ec2-54-160-143-175.compute-1.amazonaws.com
Software
ATS/9.1.10.188 /
Resource Hash
0e4b1e428a2198ef747010c094101c257b568a97cdcc0f31ed5e9868cc835b39
Security Headers
Name Value
Content-Security-Policy sandbox; default-src 'self'; script-src 'none'; object-src 'none'; report-uri http://csp.yahoo.com/beacon/csp?src=generic
X-Content-Type-Options nosniff
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-security-policy
sandbox; default-src 'self'; script-src 'none'; object-src 'none'; report-uri http://csp.yahoo.com/beacon/csp?src=generic
cache-control
no-cache, no-store, private, must-revalidate
pragma
no-cache
age
0
expect-ct
max-age=31536000, report-uri="http://csp.yahoo.com/beacon/csp?src=yahoocom-expect-ct-report-only"
x-content-type-options
nosniff
via
http/1.1 traffic_server (ApacheTrafficServer/9.1.10.188)
expires
Sat, 12 Sep 2026 12:32:19 GMT
accept-ranges
bytes
referrer-policy
strict-origin-when-cross-origin
content-length
43
date
Sat, 12 Sep 2026 12:32:19 GMT
content-type
image/gif
server
ATS/9.1.10.188
x-frame-options
DENY
POST
H3
204
/
px.ads.linkedin.com/wa/
0
0
113ms
112ms
Fetch
104.18.41.41
Cloudflare
General
Full URL
https://px.ads.linkedin.com/wa/?medium=fetch&fmt=g
Requested by
Host: snap.licdn.com
URL: https://snap.licdn.com/li.lms-analytics/insight.old.min.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.18.41.41 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Accept
*
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

linkedin-action
1
cf-cache-status
DYNAMIC
x-li-fabric
prod-lor1
x-content-type-options
nosniff
x-li-proto
http/3
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Sat, 12 Sep 2026 12:32:19 GMT
vary
Origin
priority
u=1,i
x-li-pop
cf-prod-lor1-x
strict-transport-security
max-age=31536000
access-control-allow-credentials
true
cf-ray
a39eef26fecff7b9-LAX
x-li-uuid
AAZbSGRQ1ZlQipiSrRkYTw==
access-control-allow-origin
https://www.givedirectly.org
server
cloudflare
GET
H3
200
m-outer-3437aaddcdf6922d623e172c2d6f9278.html Show response
js.stripe.com/v3/ Frame F397
200 B
1 KB
241ms
122ms
Document
text/html
3.171.38.19
Amazon.com
General
Full URL
https://js.stripe.com/v3/m-outer-3437aaddcdf6922d623e172c2d6f9278.html
Requested by
Host: js.stripe.com
URL: https://js.stripe.com/v3/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
3.171.38.19 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-171-38-19.iad61.r.cloudfront.net
Software
Cloudfront /
Resource Hash
35dcc382eb69d00369d708708cdc545f3968b68fa5bbe3e728d11fedd04f93bb
Security Headers
Name Value
Content-Security-Policy base-uri 'none'; connect-src 'self' https://r.stripe.com; default-src 'self'; font-src 'none'; form-action 'none'; frame-src https://m.stripe.network; img-src https://q.stripe.com; media-src 'none'; object-src 'none'; script-src 'self'; style-src 'self'; worker-src 'none'; report-uri https://q.stripe.com/csp-report
Strict-Transport-Security max-age=31556926; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

Referer
https://www.givedirectly.org/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

accept-ranges
bytes
access-control-allow-origin
*
age
2267
alt-svc
h3=":443"; ma=86400
cache-control
max-age=31536000
content-length
200
content-security-policy
base-uri 'none'; connect-src 'self' https://r.stripe.com; default-src 'self'; font-src 'none'; form-action 'none'; frame-src https://m.stripe.network; img-src https://q.stripe.com; media-src 'none'; object-src 'none'; script-src 'self'; style-src 'self'; worker-src 'none'; report-uri https://q.stripe.com/csp-report
content-security-policy-report-only
base-uri 'none'; connect-src 'self' https://r.stripe.com; default-src 'self'; font-src 'none'; form-action 'none'; frame-src https://m.stripe.network; img-src https://q.stripe.com; media-src 'none'; object-src 'none'; script-src 'self'; style-src 'self'; worker-src 'none'; report-uri https://q.stripe.com/csp-report
content-type
text/html; charset=utf-8
date
Sat, 12 Sep 2026 11:54:32 GMT
etag
"3437aaddcdf6922d623e172c2d6f9278"
last-modified
Fri, 11 Sep 2026 20:44:06 GMT
origin-agent-cluster
?1
server
Cloudfront
strict-transport-security
max-age=31556926; includeSubDomains; preload
timing-allow-origin
*
vary
Accept-Encoding
via
1.1 a9fbb36f9e09db412e5a358af1c8a2c6.cloudfront.net (CloudFront)
x-amz-cf-id
W0BWC3vbGj0HP_gxFf_gzR8g8C1Sc5PgwikZbwfc84ecN5Wj8HwM0A==
x-amz-cf-pop
IAD61-P7
x-cache
Hit from cloudfront
x-content-type-options
nosniff
GET
H3
200
m-outer-15a2b40a058ddff1cffdb63779fe3de1.js Show response
js.stripe.com/v3/fingerprinted/js/ Frame F397
526 B
894 B
123ms
123ms
Script
text/javascript
3.171.38.19
Amazon.com
General
Full URL
https://js.stripe.com/v3/fingerprinted/js/m-outer-15a2b40a058ddff1cffdb63779fe3de1.js
Requested by
Host: js.stripe.com
URL: https://js.stripe.com/v3/m-outer-3437aaddcdf6922d623e172c2d6f9278.html
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
3.171.38.19 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-171-38-19.iad61.r.cloudfront.net
Software
Cloudfront /
Resource Hash
ba2338aa6670580269c762f51c4291daef913201aa8f4d4fd166c1a878262652
Security Headers
Name Value
Strict-Transport-Security max-age=31556926; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://js.stripe.com/v3/m-outer-3437aaddcdf6922d623e172c2d6f9278.html
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

etag
"d96c709017743c0759cf3853d1806ba5"
age
1270
x-content-type-options
nosniff
alt-svc
h3=":443"; ma=86400
x-cache
Hit from cloudfront
x-amz-cf-id
iUYZm8ZdFQP9-rCTQlgzBkfxG0OJYZWi40cACp4gM7Ba4mp3c58vjA==
date
Sat, 12 Sep 2026 12:11:09 GMT
content-type
text/javascript; charset=utf-8
last-modified
Fri, 11 Sep 2026 01:59:06 GMT
vary
Accept-Encoding
strict-transport-security
max-age=31556926; includeSubDomains; preload
cache-control
max-age=31536000
timing-allow-origin
*
via
1.1 a9fbb36f9e09db412e5a358af1c8a2c6.cloudfront.net (CloudFront)
accept-ranges
bytes
access-control-allow-origin
*
content-length
526
x-amz-cf-pop
IAD61-P7
server
Cloudfront
GET
H2
200
inner.html Show response
m.stripe.network/ Frame CFE1
930 B
1 KB
292ms
116ms
Document
text/html
151.101.0.176
Fastly
General
Full URL
https://m.stripe.network/inner.html
Requested by
Host: js.stripe.com
URL: https://js.stripe.com/v3/fingerprinted/js/m-outer-15a2b40a058ddff1cffdb63779fe3de1.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.0.176 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
Fastly /
Resource Hash
92844e6b1ad5890a9e5e4b9dfb7abdb37dca64e8ca7365052c9d2fc8103c349d
Security Headers
Name Value
Content-Security-Policy base-uri 'none'; connect-src https://m.stripe.network https://m.stripe.com; default-src 'none'; font-src https://m.stripe.network https://fonts.gstatic.com; form-action 'none'; frame-src https://m.stripe.network https://js.stripe.com; img-src https://m.stripe.network https://m.stripe.com https://b.stripecdn.com; script-src https://m.stripe.network 'sha256-e357n1PxCJ8d03/QCSKaHFmHF1JADyvSHdSfshxM494=' 'sha256-5DA+a07wxWmEka9IdoWjSPVHb17Cp5284/lJzfbl8KA=' 'sha256-/5Guo2nzv5n/w6ukZpOBZOtTJBJPSkJ6mhHpnBgm3Ls='; style-src https://m.stripe.network; report-uri https://q.stripe.com/csp-report
Strict-Transport-Security max-age=31556926; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

Referer
https://js.stripe.com/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

accept-ranges
bytes
age
297
alt-svc
h3=":443";ma=86400,h3-29=":443";ma=86400,h3-27=":443";ma=86400
cache-control
max-age=300, public
content-encoding
br
content-length
438
content-security-policy
base-uri 'none'; connect-src https://m.stripe.network https://m.stripe.com; default-src 'none'; font-src https://m.stripe.network https://fonts.gstatic.com; form-action 'none'; frame-src https://m.stripe.network https://js.stripe.com; img-src https://m.stripe.network https://m.stripe.com https://b.stripecdn.com; script-src https://m.stripe.network 'sha256-e357n1PxCJ8d03/QCSKaHFmHF1JADyvSHdSfshxM494=' 'sha256-5DA+a07wxWmEka9IdoWjSPVHb17Cp5284/lJzfbl8KA=' 'sha256-/5Guo2nzv5n/w6ukZpOBZOtTJBJPSkJ6mhHpnBgm3Ls='; style-src https://m.stripe.network; report-uri https://q.stripe.com/csp-report
content-type
text/html; charset=utf-8
date
Sat, 12 Sep 2026 12:32:19 GMT
etag
"441070f07f0e89a26ecd81c9afcab8ed"
last-modified
Wed, 10 Sep 2025 21:05:01 GMT
server
Fastly
strict-transport-security
max-age=31556926; includeSubDomains; preload
vary
Accept-Encoding, Origin
via
1.1 varnish, 1.1 varnish
x-cache
HIT, HIT
x-cache-hits
2574405, 71
x-content-type-options
nosniff
x-request-id
4ab00363-16cb-466e-ab76-67c5fa105c19
x-served-by
cache-chi-kmdw8640036-CHI, cache-bur-kbur8200084-BUR
x-timer
S1789216340.780740,VS0,VE0
GET
H2
200
out-4.5.45.js Show response
m.stripe.network/ Frame CFE1
87 KB
14 KB
66ms
65ms
Script
text/javascript
151.101.0.176
Fastly
General
Full URL
https://m.stripe.network/out-4.5.45.js
Requested by
Host: m.stripe.network
URL: https://m.stripe.network/inner.html
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.0.176 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
Fastly /
Resource Hash
f2a8a36c74c59cfbe7a73d441cfd180ca6e6a9942a74ef9b240191d1c6056a59
Security Headers
Name Value
Strict-Transport-Security max-age=31556926; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://m.stripe.network/inner.html
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-request-id
d29f58fc-d1ef-429b-9c30-8101e30ef6de
content-encoding
br
etag
"f4d61b273ea36d2e71ce1a601ab0caa2"
age
157
x-content-type-options
nosniff
alt-svc
h3=":443";ma=86400,h3-29=":443";ma=86400,h3-27=":443";ma=86400
x-cache
HIT, HIT
date
Sat, 12 Sep 2026 12:32:19 GMT
last-modified
Wed, 10 Sep 2025 21:05:01 GMT
content-type
text/javascript; charset=utf-8
x-cache-hits
311901, 39
x-served-by
cache-chi-klot8100134-CHI, cache-bur-kbur8200084-BUR
strict-transport-security
max-age=31556926; includeSubDomains; preload
vary
Accept-Encoding, Origin
cache-control
max-age=300, public
x-timer
S1789216340.907526,VS0,VE0
via
1.1 varnish, 1.1 varnish
accept-ranges
bytes
content-length
14184
server
Fastly
POST
H2
200
6 Show response
m.stripe.com/ Frame CFE1
156 B
580 B
377ms
140ms
XHR
application/json
44.232.203.244
Amazon.com
General
Full URL
https://m.stripe.com/6
Requested by
Host: m.stripe.network
URL: https://m.stripe.network/out-4.5.45.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
44.232.203.244 Boardman, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-44-232-203-244.us-west-2.compute.amazonaws.com
Software
nginx /
Resource Hash
a9193773d856bb041f0fe767f4fb54278b83c6590442d90cf12ed2abfd82ac5c
Security Headers
Name Value
Strict-Transport-Security max-age=31556926; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://m.stripe.network/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31556926; includeSubDomains; preload
x-stripe-proxy-response
upstream
access-control-allow-credentials
true
x-content-type-options
nosniff
x-stripe-server-rpc-duration-micros
2494
access-control-allow-origin
https://m.stripe.network
content-length
156
date
Sat, 12 Sep 2026 12:32:20 GMT
content-type
application/json;charset=utf-8
server
nginx
access-control-allow-headers
Content-Type
GET
H3
200
favicon.svg
www.givedirectly.org/wp-content/themes/givedirectly/img/favicon/
1 KB
1 KB
197ms
197ms
Other
image/svg+xml
13.35.78.128
Amazon.com
General
Full URL
https://www.givedirectly.org/wp-content/themes/givedirectly/img/favicon/favicon.svg
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
13.35.78.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-35-78-128.iad61.r.cloudfront.net
Software
Apache/2.4.68 (Debian) /
Resource Hash
7df19dfbc61ae66e6bc49a2e88c40833f3f957bf6d02bca86f8525c669905610
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/liberia
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
vary
Accept-Encoding
cache-control
public, max-age=60, stale-while-revalidate=300
content-encoding
br
via
1.1 090bf7e9d88c922b92daac177304afaa.cloudfront.net (CloudFront)
alt-svc
h3=":443"; ma=86400
x-cache
Miss from cloudfront
x-amz-cf-id
SRy1d2YCx1YZsurlofzNeAK5-420wQBWgJqEi4VAp-jOiqDbEaA8EQ==
date
Sat, 12 Sep 2026 12:32:20 GMT
content-type
image/svg+xml
x-amz-cf-pop
IAD61-P11
server
Apache/2.4.68 (Debian)
last-modified
Fri, 28 Aug 2026 07:48:46 GMT
x-frame-options
DENY
POST
H3
200
log_event Show response
www.youtube.com/youtubei/v1/ Frame 0D77
28 B
50 B
93ms
89ms
XHR
application/json
142.251.157.119
Google LLC
General
Full URL
https://www.youtube.com/youtubei/v1/log_event?alt=json
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywHdVJjs6ktwWXG8Pg3CpN4ZEVjBaQ/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.157.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
scaffolding on HTTPServer2 /
Resource Hash
d7d5e54ad1e33d7ab49c664323ced79cb9723ff15e9764cd0edc3e15208e8336
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
X-YouTube-Client-Name
56
X-YouTube-Ad-Signals
dt=1789216337978&flash=0&frm=2&u_tz=-600&u_his=1&u_h=1200&u_w=1600&u_ah=1200&u_aw=1600&u_cd=24&bc=31&bih=-12245933&biw=-12245933&brdim=190%2C190%2C190%2C190%2C1600%2C0%2C1600%2C1200%2C529%2C298&vis=1&wgl=true&ca_type=image
X-Goog-Event-Time
1789216341007
X-YouTube-Client-Version
2.20260911.01.00
Content-Type
application/json
X-YouTube-Page-Label
youtube.embeds.web_20260911_01_RC00
X-YouTube-Page-CL
979642621
X-YouTube-Utc-Offset
-600
Referer
https://www.youtube.com/embed/mCsv_yLgi3c?start=1&feature=oembed&enablejsapi=1&origin=https%3A%2F%2Fwww.givedirectly.org
X-YouTube-Device
cbr=Chrome&cbrver=153.0.0.0&ceng=WebKit&cengver=537.36&cos=X11&cplatform=DESKTOP
X-Goog-Visitor-Id
CgtrNHB3SmNwYnowdyjRjJXVBjIKCgJVUxIEGgAgT2LfAgrcAjIxLllUPVdieHRiUTlLZi1lNmFELXo4VmotY3pJRElMMWd0RVl4OENIUVAydEswbDd0Wk1TdGRUcmM5OXl0QkFQZlctcGctWXRqQWVFWE1lVnhxLUVER19yLXpncXNwTVdrQVlSVmgya280YkRhbFRDdERlbjBXWm95MXNsZzZJYlN0UF9EVEVzd2ZPbHNvdzZwRnlacVZwY2xuYmlBVGc1OUI0X3czY21HTmozWjVmaFJzRmZmNXNjallKUVBfWEU2WkR6VzRrdUcwbm1ITmE5eWhCVTc5SWtDeGdvNFdZV01QejdiWU5pcjRid3kwc1lvM3RIM0JuSkNSdnlrM0lfdjBQUHpZNlUzZDE5NE5OOUFjcmVVTVJpd0Q1QVF5Zk5nX3lQdFpWYUJvVUZ5TXVuZFQ0OUhGM2t6SGVsNmEzV245ZTNJejc0aFk5YVZweWlOVTYxeWtJb25rQQ%3D%3D
X-Goog-Request-Time
1789216341007
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
X-YouTube-Time-Zone
Pacific/Honolulu

Response headers

content-encoding
br
x-content-type-options
nosniff
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
31
date
Sat, 12 Sep 2026 12:32:21 GMT
x-xss-protection
0
content-type
application/json; charset=UTF-8
vary
Origin, X-Origin, Referer
server
scaffolding on HTTPServer2
x-frame-options
SAMEORIGIN
POST
H2
204
collect
analytics.google.com/g/
0
0
132ms
131ms
Fetch
text/plain
142.251.163.113
Google LLC
General
Full URL
https://analytics.google.com/g/collect?v=2&tid=G-GV8XF9FJ16&gtm=45je6992v870284789z8812195104za20gzb812195104zd812195104&_p=1789216336517&gcd=13l3l3l3l1l1&npa=0&dma=0&_eu=AAAAAGQC&cid=1664461639.1789216338&frm=0&pscdl=noapi&rcb=8&sr=1600x1200&uaa=x86&uab=64&uafvl=Chromium%3B153.0.0.0%7CGoogle%2520Chrome%3B153.0.0.0%7CNot_A%2520Brand%3B8.0.0.0&uam=&uamb=0&uap=Linux&uapv=&uaw=0&ul=en-us&gaf=2&_s=2&tag_exp=115616985~115938465~115938468~118131809~118897920~118897930~120213116~120385423~120469145~120469153~120847433~120912438&sid=1789216337&sct=1&seg=0&dl=https%3A%2F%2Fwww.givedirectly.org%2Fliberia&dt=Cash%20Aid%20in%20Liberia%20%7C%20GiveDirectly&en=10%25%20scroll&gap.plf=5&_et=1423&tfd=13556
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtag/js?id=G-GV8XF9FJ16&cx=c&gtm=4e6992
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.163.113 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
wv-in-f113.1e100.net
Software
Golfe2 /
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.givedirectly.org/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, no-store, must-revalidate
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
content-security-policy-report-only
script-src 'none'; form-action 'none'; frame-src 'none'; report-uri https://csp.withgoogle.com/csp/scaffolding/ascnsrsggc:197:0
report-to
{"group":"ascnsrsggc:197:0","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/scaffolding/ascnsrsggc:197:0"}],}
expires
Fri, 01 Jan 1990 00:00:00 GMT
access-control-allow-origin
https://www.givedirectly.org
cross-origin-opener-policy-report-only
same-origin; report-to=ascnsrsggc:197:0
content-length
0
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sat, 12 Sep 2026 12:32:24 GMT
content-type
text/plain
server
Golfe2

Failed requests

These URLs were requested, but there was no response received. You will also see them in the list above.

Domain
www.youtube.com
URL
https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywHdVJjs6ktwWXG8Pg3CpN4ZEVjBaQ/m=root,base

Verdicts & Comments Add Verdict or Comment

56 JavaScript Window variables

These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.

object| 0 object| 1 object| dataLayer boolean| consentForPostHogLogging object| posthog function| genesisBlocksShare function| $ function| jQuery number| CONSENT_EXPIRY_SEC string| CONSENT_DATE string| CONSENT_FLAG function| isOptedOut function| hasValidConsentDate function| setConsentDate function| setConsentFlag function| firstTime function| parseCookies function| setCookie function| removeCookie function| setLastDonationId object| cookies function| Popper object| Util object| bootstrap function| Tooltip function| Popover object| Cookies function| Waypoint string| sitedomain string| siteprotocol string| siteaddress string| waypointContextKey object| __PosthogExtensions__ object| webpackChunkStripeJSouter function| noop function| Stripe object| _POSTHOG_REMOTE_CONFIG object| google_tag_manager object| google_tag_data string| _linkedin_data_partner_id function| fbq function| _fbq object| dotq function| onYouTubeIframeAPIReady function| extendPostHogWithSurveys object| gaGlobal object| GooglebQhCsO object| scriptUrl object| ttPolicy object| YT object| YTConfig function| onYTReady object| YAHOO function| lintrk boolean| _already_called_lintrk object| ORIBILI
28 Cookies

Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.

Domain/Path Expires Name / Value
.givedirectly.org/ 1970-01-22
02:36:16
Name: consented_date_gd_web
Value: 1789216336604
.givedirectly.org/ 1970-01-22
02:36:16
Name: consented_opt_out_gd_web
Value: false
.youtube.com/ 1969-12-31
23:59:59
Name: YSC
Value: 6Mw204_ubxI
.youtube.com/ 1970-01-21
21:19:28
Name: VISITOR_INFO1_LIVE
Value: k4pwJcpbz0w
.youtube.com/ 1970-01-21
21:19:28
Name: VISITOR_PRIVACY_METADATA
Value: CgJVUxIEGgAgTw%3D%3D
.givedirectly.org/ 1970-01-22
01:45:52
Name: ph_phc_j1Fm3HqKiplMs7guXcEKIdcYC8CQCUOu31quq5YpXFj_posthog
Value: %7B%22%24device_id%22%3A%2201a0959a-aca0-7414-8a94-0e9d56b8a5b6%22%2C%22distinct_id%22%3A%2201a0959a-aca0-7414-8a94-0e9d56b8a5b6%22%2C%22%24sesid%22%3A%5B1789216337064%2C%2201a0959a-acb4-7e52-951a-ee71e906ef19%22%2C1789216337064%5D%2C%22%24epp%22%3Atrue%2C%22%24initial_person_info%22%3A%7B%22r%22%3A%22%24direct%22%2C%22u%22%3A%22https%3A%2F%2Fwww.givedirectly.org%2Fliberia%22%7D%2C%22%24user_state%22%3A%22anonymous%22%7D
.givedirectly.org/ 1970-01-21
18:27:52
Name: Checkout_long_session
Value: eyJpdiI6IllmSFJKQi9BbHJ2T2c4YW5sMk5KYmc9PSIsInZhbHVlIjoidFZHZ0tacGYvVkZRbTdVQnNlSTl1dzdzMWIrNGhYM2tZTkZ1dnJEVXNWU2dSWWlDcXpiUkJQYlYranF0aXFnSzA0NlEwZ2R5Nk05WnlHSzJWTXczZVRJdURKRXlCSGo3b3pUb3VaRWlYYmlIdnJkaXlNZStsUXA1ck5SbDV3c1oiLCJtYWMiOiIwZjY5ZGI2YzA2MDljNGNhMzM5M2FlNTFmNzU4ZjQ1ZGRiYTFlYjk3NTUzNDFmNjk0YTZmZDViMzY0NWFhYWVkIiwidGFnIjoiIn0%3D
.givedirectly.org/ 1970-01-21
17:01:42
Name: XSRF-TOKEN
Value: eyJpdiI6InRaNTlxM0dPVERleWZSQjFSbTUwcFE9PSIsInZhbHVlIjoieDFoNzJiM3JSbmszT1N6YkpjT2wzRFd5QkViL3VCYXNJelJMZ1kwM3NJMWdkeWtGNC82dnp6bjc3c1pWMHpWbm5GYktnbU1lREVYaUIzU0ZzeE5ERDNvc3NlYjlsTjIwRUFDcWZBUkZLN3dUNnROLzJkUjBESnQ2VkdYMFdnQ2YiLCJtYWMiOiJjNzViY2IyYWM4NjdiMjMyMDhmYjQxMjQ3N2YxYWY4MjYwZjQ3YTMxZDc5Yjc2MWNlZGI0OTY2ODEwODdhYjQzIiwidGFnIjoiIn0%3D
.givedirectly.org/ 1970-01-21
17:01:42
Name: checkout_session
Value: eyJpdiI6IkFOTTU5QlMwZktXbnd0eHo5UkhoS2c9PSIsInZhbHVlIjoiL0pJbnJNS2FMR01SeHFuS0hQL2luUU9nUTdJejIrMkhGVk1JZ0Q0MnFtT1UvUXdESWdsVk1NbzMzaGdkMUZKRFIwVTVtQ2YzZk51SlhQRUhyNTBWRTUrbmZVeGg3d0lFODhVQllERDg3RVpld1VWMEs5Rll5SGN3YkY2S2RaQlUiLCJtYWMiOiIyZDZmYmZhNGI5YTNiMmQ1ZGI3ZmI0NzMwZmY0NzllMjk5OTAzNTBlYTY0NjVlZmVkNGI3N2Y5NDU0MWI3OGYzIiwidGFnIjoiIn0%3D
.givedirectly.org/ 1970-01-21
19:09:52
Name: _gcl_au
Value: 1.1.1823712742.1789216337
.givedirectly.org/ 1970-01-22
02:36:16
Name: _ga
Value: GA1.1.1664461639.1789216338
.youtube.com/ 1970-01-21
21:19:28
Name: __Secure-YNID
Value: 21.YT=klkXI4aKEg_YXWiwQaODQ-wy74UAOxs2m_Xbg2RYdZF8KPYPLzqqciikbyECWHVWmNe3zAX-S1iNbHi5H2s0Lvtmv9ucUBKZ61EUtxvms1PcbJzZF9RqyPCycXyec0ZDTAfHz7pKHQpX0fVOqRcwMA9nQA18THbJyl7gkKCrNfHUQB69C7o1NvUilwa6yHjljoYP4aSH0XrbOBaBq8u6AS2KlbtMjNz1d8cZwzAzIL-X_fldkKdeCerWKBj-HYtPsOqe5YLinS1rXSIRf6bjHDVFRvOpe5xg_rrTwdhMgx8tLQR8x7G7zksTjwbllNFSgZPrLKKUw4xUkM29X2TJMQ
.youtube.com/ 1970-01-21
21:19:28
Name: __Secure-ROLLOUT_TOKEN
Value: CNaDhpnU2su7lQEQzbzBoYbplgMYieXuoYbplgM%3D
.doubleclick.net/ 1970-01-21
17:00:17
Name: test_cookie
Value: CheckForPermission
.givedirectly.org/ 1970-01-21
19:09:52
Name: _fbp
Value: fb.1.1789216338219.92955045817569586
.facebook.com/ 1970-01-21
19:09:52
Name: fr
Value: 0etabxdIl549uILDN..BqpUZS...1.0.BqpUZS.AWcapyTw_lU5cqy6m0_-RPpMqfc
.linkedin.com/ 1970-01-21
19:09:52
Name: li_sugr
Value: 3708e579-8524-4359-90b0-488c36f12230
.linkedin.com/ 1970-01-22
01:45:52
Name: bcookie
Value: "v=2&db3dfe4e-294f-4a57-8f07-bf6aa74de6ea"
.linkedin.com/ 1970-01-21
17:01:42
Name: lidc
Value: "b=OGST06:s=O:r=O:a=O:p=O:g=3596:u=1:x=1:i=1789216338:t=1789302738:v=2:sig=AQGn5jRxONUGFDIkZJx6LFHq4QdmSkVj"
.linkedin.com/ 1970-01-21
17:00:18
Name: __cf_bm
Value: u1Ah_Bfyvt2qdzd618fP3fezZjakEvNNSHY_7kYFG3w-1789216338.5592122-1.0.1.1-KCX5i1qPP3us9zZgpikantW3tLsSi5750Ddq5.__p5F.Elaxvyjo4vMi6amTjE5HucBIJCj0e90FzR7SQbdTIlKpuG8NQ3druV3jgtvAt1F.kBm5gYHo.6OaShed56ih
.linkedin.com/ 1970-01-21
17:43:28
Name: UserMatchHistory
Value: AQIS_4IPLw8GhgAAAaCVmrMLlNm_SoVqQkBDdeOxa9nssnuwmqls0-Uis_cspdj3StfkD37Jad36aA
.linkedin.com/ 1970-01-21
17:43:28
Name: AnalyticsSyncHistory
Value: AQL0EvmevXnRhgAAAaCVmrML_avTgYRX5OKJ4Jt-ctGCb03A3k_2rw1mo9zIMtSfD7-f-iIsHj6QawlStPQV_Q
.www.linkedin.com/ 1970-01-22
01:45:52
Name: bscookie
Value: "v=1&20260912123218672c99ea-2cd2-42be-8d35-480306bca036AQFNUh8Dc9ZLZyKBaxkz50kRojoKy1Yq"
.yahoo.com/ 1970-01-22
01:46:13
Name: A3
Value: d=AQABBFNGpWoCEBzhrjx_pWmk6P0cm3n-iKQFEgEBAQGXpmqvatwr0iMA_eMDAA&S=AQAAAmqIcJ9BTyFWFXALDwfQeNA
.givedirectly.org/ 1970-01-22
02:36:16
Name: _ga_GV8XF9FJ16
Value: GS2.1.s1789216337$o1$g0$t1789216339$j58$l0$h0
m.stripe.com/ 1970-01-22
02:36:16
Name: m
Value: 46d7834e-ca5d-4435-83d6-2dce4866c701352616
.www.givedirectly.org/ 1970-01-22
01:45:52
Name: __stripe_mid
Value: d22a2eee-fdcd-4659-9b9c-b3587da1e831b6fb3d
.www.givedirectly.org/ 1970-01-21
17:00:18
Name: __stripe_sid
Value: aeb051ea-f2a8-446e-9045-0e3a15083204c338cd

3 Console Messages

A page may trigger messages to the console to be logged. These are often error messages about being unable to load a resource or execute a piece of JavaScript. Sometimes they also provide insight into the technology behind a website.

Source Level URL
Text
other warning URL: https://www.givedirectly.org/liberia(Line 1166)
Message:
Unrecognized feature: 'web-share'.
rendering warning URL: https://www.youtube.com/embed/mCsv_yLgi3c?start=1&feature=oembed&enablejsapi=1&origin=https%3A%2F%2Fwww.givedirectly.org
Message:
[]Automatic fallback to software WebGL has been deprecated. Please use the --enable-unsafe-swiftshader flag to opt in to lower security guarantees for trusted content.
rendering warning URL: https://www.youtube.com/embed/mCsv_yLgi3c?start=1&feature=oembed&enablejsapi=1&origin=https%3A%2F%2Fwww.givedirectly.org
Message:
No available adapters.

Security Headers

This page lists any security headers set by the main page. If you want to understand what these mean and how to use them, head on over to this page

Header Value
Strict-Transport-Security max-age=31536000
X-Frame-Options DENY

Indicators

This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.

ad.doubleclick.net
ajax.googleapis.com
analytics.google.com
connect.facebook.net
donate.givedirectly.org
erinaceus.givedirectly.org
fonts.googleapis.com
fonts.gstatic.com
googleads.g.doubleclick.net
i.ytimg.com
jnn-pa.googleapis.com
js.stripe.com
m.stripe.com
m.stripe.network
p.typekit.net
px.ads.linkedin.com
s.yimg.com
snap.licdn.com
sp.analytics.yahoo.com
static.doubleclick.net
stats.g.doubleclick.net
use.typekit.net
www.educationliberia.org
www.facebook.com
www.givedirectly.org
www.google.com
www.googletagmanager.com
www.gstatic.com
www.linkedin.com
www.youtube.com
yt3.ggpht.com
www.youtube.com
104.18.41.41
13.35.78.128
142.250.31.94
142.251.151.119
142.251.153.4
142.251.157.119
142.251.163.113
142.251.163.95
142.251.167.155
142.251.167.157
142.251.179.97
151.101.0.176
172.217.114.4
172.253.139.148
172.253.62.119
18.238.49.55
192.178.155.132
192.178.155.154
192.178.155.95
192.178.218.148
192.179.24.94
23.215.0.138
23.215.0.145
23.55.176.231
3.167.69.84
3.171.38.13
3.171.38.19
44.232.203.244
52.216.10.178
54.160.143.175
57.144.70.1
57.144.70.128
69.147.92.11
00c92e62c4c10775a27a8085d8646d8e439f900de55097bb1daac2ee87b2c887
00ee80c3c37a18583b552a3c13e1a336a3ca6e8e24048a96a6983475b5f9a033
0985d5b9720cf359347e5c471165fe3e9c1e069caa2e4bd213ac038c562c36ea
09d305a5a1c4756015b5b0c509dcc3f121a6e9a754a92ed5bacbb5a60899d411
0c40bafcfdc8adc6db63a6a5bfdb3dd5201798e6163fc674dc2fcbdb2a4134f1
0e4b1e428a2198ef747010c094101c257b568a97cdcc0f31ed5e9868cc835b39
0f0024b428a219528079eb53d4a21f8e1b8893d0bec5bdfadb24e7fffb3954ec
0fe8e60934edbcf8df2542daca0fa414584ccc54bcee57427a4da51dbc98df2e
11ec04e3948e25a0d78d2f77c04940b8e38a086624ec36fa4605a2a69b133e94
1c0ff118a4290c99f39c90abb38703a866e47251b23cca20266c69c812ccafeb
1e6f131e5c23998532caa01dec741cd746efdb7364cffaf33a43f227aaa0d458
1f4513a435d6a3047d20a50c1e7d4263de42146c74be227f774b5e82e6357e75
20b25217b834eba7ea0d181ff947366a220af18719c76e19ac66672d63d95cd8
20b535fa80c8189e3b87d1803038389960203a886d502bc2ef1857affc2f38d2
2236b2368aeb6841735bbb7901ef75dca8ca81e24464aa0d9dcfec79d272e74d
246646a9adecc53ddd648f6073306ccb3ad17e926d9ef5ccfffd6975c092feb5
27b14e9c51de61009538b1b24a725ae1105f6893df957f8da3003ab6ab076cd4
2976fbc22a5a7339d5278e01608d61c4f56a5d20165cafb51ae25d7802bb96f6
29d59026f0ea9a78effd5cb8a2d175865f2f045b9d49287c10cf443dbe8e4bbb
2c295d99e26dcf357d4d01bcf270fd6924b600c9a13dd8c363ef114f4c6976fa
309a867ab2e3ac2fa076db478f9d39b8de5e9e4d44aecd02866dc89f8f333653
32c7feeabbc5ff335db9b1c6c4a22b52cec693725f2506f75f08886aadbc5cb4
35dcc382eb69d00369d708708cdc545f3968b68fa5bbe3e728d11fedd04f93bb
3a941464f4e01d9137623bb3a3f96edf759c910a6d282c4f1d59b56caaf40398
41e9a6b19ec412ee545368d266fcea578cb95540a55cde8e743000b0f7b28fdc
44136fa355b3678a1146ad16f7e8649e94fb4fc21fe77e8310c060f61caaff8a
44343d3cafbec3175a2ec435bdf729f169a1829a06e11a5fbdf1e8656eac2052
48d92412103b1917917fad43511a9864e977f89423a823d94450bffa3ee6898d
529b5b205dcd5ab2c9e1d1308fee462193f4d8b3524e36ba58d0609868ffb31c
555e95e5af65cfd867790ac83d0f93780e6a63078135648b21c4fb935c1e04b0
62f3f809487194fcc55a3ebd88811a604ae496027bb425d4ebd15d9ae1921945
66f0389d96a9067eb312d1307dbbecaba0ca19011d387de0f0e7e19acb993bc4
67a7d9f64d1fd0d1000a3ad434cdead195b8394f17d47ec936087450febc5d3b
6aa8b7c94c8dd93a37474c0fe40fcde67fcac48cf0faebc6d8f96c8d843ccd88
6cfea94a47e78a421a9bab12ab484dc77fb3ea83d340d43946d96fd0ab31219f
6fa88a20839537ae66da730e5bd183035265176d972bc8df075b89da0c6186ea
717f6bb5f6cc69c444f54376a72dee0ca7968b2a12e7c9475247ec85c0e75a53
7b17d6832b35cc032a658ba6b45c1538ce968b838d55d9919de6ffa976935a98
7bd45ce8a39f954d4ca2c3da0c86ec3c772896313952e80abb669fe211c8a24f
7df19dfbc61ae66e6bc49a2e88c40833f3f957bf6d02bca86f8525c669905610
7e7a3bbb1955e053b838b91c6659278d2c987a068aed0b9e93a438a071f84709
83346941cce56b0970f9ea40ab23b100df1a123c1c0b1d33ab7fc062fba40767
86b742cfa596799c1a5856ba629afdd7b7b1e5478112bbb2101d126b9a2c75d9
89f55bf8dd225e51c1e21e7ca14b27aa21585b36ccf83073295c2468b15390da
8aec898354f84b41bf1d16161007cd4e617214da33db3b09f85e485e20374d61
8ce1e057fd8095e3d4e922d96710396c5df686cea4c532884429575e574784b7
90de1f3d11a5a315fe41d6d87a897bd2f8f3bdc836eac6040f19649e49ac1adb
9239979ee19c4362f6fbb3be5c4f02b04b17f25272ba02b490d9ff904aa446f9
92844e6b1ad5890a9e5e4b9dfb7abdb37dca64e8ca7365052c9d2fc8103c349d
954899c87da3edf57f4a4ebcf228972d176df05e1ff9f0cb212eda0b906eae97
95682117b2f72a2b381c725cbbf2fb87404b954781c2c32764595eab7fb6af89
9719b92698fc9da98e2054c27e8c540db6d375791d68c686d48f1fb8584886a9
9743811b64846226fe68de5850229c713828eb05de3d9d6172462b64b07a63b7
97a50332c2d8403e8bb2a89c563a0ab9c66cd5bb77a855aebd6c6b13864b54a3
9a6f174d593d8404d55c3ba5b8ddc199d63196b87c1cf40b061fe0266660af3d
9b3a1ff454f7410838e773a7640b9bccc0bae845f4c4fe5daf03c11d60a9613b
9baa573e4378873b7ac81ccb1d954ce9bb2b1a933947ad3012263ddc604d8505
9cbea185b2208b219f0b0137ff09375b5ea40735b46e36587ec1aaef44875a95
9d66ed39cd90111abe8be07798b65f01076983dcead837eada3c68219e1cd383
9f17a11aa8e2908c07d47b7ce57df686a9cff242515da2f997d41147a8282b26
a137b03188828d7472172a0c125abd40fee264778eac775dcbd8b528b0b62fa6
a29773a5a18b27354f0fc08df3705cb3606615e255f3321f791294cbe630c40e
a9193773d856bb041f0fe767f4fb54278b83c6590442d90cf12ed2abfd82ac5c
ad1ee1351e9e831c255405b95cef5279f74119e03464a23093e59f513e6f2aa0
aeedeaed40dc6edcad6abb1e8444f5660d51467cb00b3c64aa3a9f09fb2402d6
af0745562f1d597413e728a7ddaf2513e7385c4fa3a1ad800e8aa70128aad4cc
af5095668b522414e145df421c68f974dd4c9484c43a5f0884633458cb38bbd2
b617a5a17c7568b46b5e2a514917282e709eef137fe4d673f31224bcc13fcdd0
b8564dc4cdc772344d2b96e0e0e7cd934d7d01793439edb5716cf5d1b879995d
b944b9469a2b4f007755ac5c43b4101d568cbcd2bda8f20f725ebb90e64674ea
ba2338aa6670580269c762f51c4291daef913201aa8f4d4fd166c1a878262652
bad45c3fb085c6b8a5840059d3a5abbe0205a9e44ac0fb5153a82b1030e0dfe0
bd56a479237f7212eae3a46a3f0e9aeba7dff44dab300249a18fa24587fb63d0
bd7f7c0f0d2c857c1981dae1c9224ba44a6e0c8baff8d2b0b30362694235b3ec
c2dcf46501a48a87a7859596834012e81569a181f7b80bda4d91b04798f84751
c56bfcd8aa023d34a83bb9bbac9cd2325cf6bef3f357f0bd86a33dbcc905027e
d489b866f669f2f15392d5cdce4b6e23f9e66fd7e0f38155510282f5e68c8ec2
d68b224c0e01b62d9384bdf1a607c3c128b67b632ae093efc8a393d8592de242
d692a67352a3dfa80010c86a62761cfff05c0b1086618106a8576cc45a6a8115
d7d5e54ad1e33d7ab49c664323ced79cb9723ff15e9764cd0edc3e15208e8336
d8f9afbf492e4c139e9d2bcb9ba6ef7c14921eb509fb703bc7a3f911b774eff8
de5e3ac842421180e0fd836bdaf1e1f93216d501fc5800b429797f53956d1d35
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
e7e6649d05d4e8097557de6ae15ba06fb174da2ffdb5010788aae11b25ffcf01
eb14baeac955bb11e33cd7fd3fd2f698cf20db1b450325f45ea843b6cdc82366
ed01bb186cdaa0069b86a9e3f983af5ee155ffd95bfa07d028a079e4fa15e31d
eed0dc1fdb5d97ed188ae16fd5e1024a5bb744af47340346be2146300a6c54b9
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
f2a8a36c74c59cfbe7a73d441cfd180ca6e6a9942a74ef9b240191d1c6056a59
f43939258cf629ebe3373bba92cce6cd86f5d8aab6e5cfe52ca161ad831622ac
f5b96378649f8a8c7e7e2ee18beafbf373b305acb34dd73be52682b08f48b6de
f8a26c88ffc70bb0b322ae2df632fbbaaafeec0702b2e808fd8b5358fd8880a8
fd9f80224f30051fc4480a89d25c328781f3de66f17d8624037977f65c8e7fcf
fe87d870bd269d4c16c574da5b843f13cbe4722fb824a87eb8b3a162c0330a26