
godisaweapontour-com-github-io.pages.dev
172.66.44.152
Public Scan
Open in
urlscan Pro
https://godisaweapontour-com-github-io.pages.dev/ 1yr old
Submission: On September 13 via automatic, source certstream-suspicious (September 13th 2026, 3:13:28 am UTC) — Scanned from CA Go Pro
Only in urlscan Pro
- Select different country locations for Private Scans.
- Use a global network of additional scanning locations and residential IPs for scanning.
- Interact with pages while you are scanning them.
- Download files from remote websites.
- Scan websites on the Tor Network.
Summary
TLS certificate: Issued by WE1 on September 13th 2026. Valid for: 3mo.
This is the only time godisaweapontour-com-github-io.pages.dev was scanned on urlscan.io!
urlscan.io Verdict: No classification
Domain & IP information
| IP Address | AS Autonomous System | ||
|---|---|---|---|
| 19 | 172.66.44.152 172.66.44.152 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 142.251.167.95 142.251.167.95 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 151.101.3.42 151.101.3.42 | 54113 (FASTLY) (FASTLY - Fastly) | |
| 6 | 142.251.151.4 142.251.151.4 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 2 | 172.253.62.94 172.253.62.94 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 20 | 23.209.72.174 23.209.72.174 | 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.) | |
| 1 | 23.219.161.116 23.219.161.116 | 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.) | |
| 1 2 | 142.250.31.156 142.250.31.156 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 142.251.163.149 142.251.163.149 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 3 | 23.193.201.53 23.193.201.53 | 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.) | |
| 4 | 142.251.151.119 142.251.151.119 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 3 | 34.160.81.0 34.160.81.0 | 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC) | |
| 2 | 35.186.224.24 35.186.224.24 | 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC) | |
| 1 | 142.251.167.119 142.251.167.119 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 5 | 35.186.224.9 35.186.224.9 | 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC) | |
| 2 | 172.217.116.4 172.217.116.4 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 73 | 17 |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| godisaweapontour-com-github-io.pages.dev 1yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: ww-in-f95.1e100.net
| fonts.googleapis.com 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: bc-in-f94.1e100.net
| fonts.gstatic.com 10yr old |
ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL)
PTR: a23-209-72-174.deploy.static.akamaitechnologies.com
| embed-cdn.spotifycdn.com 3yr old |
ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL)
PTR: a23-219-161-116.deploy.static.akamaitechnologies.com
| image-cdn-ak.spotifycdn.com 3yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: bj-in-f156.1e100.net
| googleads.g.doubleclick.net 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: wv-in-f149.1e100.net
| static.doubleclick.net 10yr old |
ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL)
PTR: a23-193-201-53.deploy.static.akamaitechnologies.com
| encore.scdn.co 6yr old |
ASN15169 (GOOGLE - Google LLC, US)
| www.google.com 14yr old | |
| www.youtube.com 10yr old |
ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US)
PTR: 0.81.160.34.bc.googleusercontent.com
| o22381.ingest.us.sentry.io 2yr old |
ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US)
PTR: 24.224.186.35.bc.googleusercontent.com
| apresolve.spotify.com 9yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: ww-in-f119.1e100.net
| i.ytimg.com 10yr old |
ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US)
PTR: 9.224.186.35.bc.googleusercontent.com
| gue1-spclient.spotify.com 4yr old |
| Apex Domain Subdomains |
Transfer | |
|---|---|---|
| 21 |
spotifycdn.com
embed-cdn.spotifycdn.com — Cisco Umbrella Rank: 18808 3yr old image-cdn-ak.spotifycdn.com — Cisco Umbrella Rank: 3122 3yr old |
666 KB |
| 19 |
pages.dev
godisaweapontour-com-github-io.pages.dev 1yr old |
3 MB |
| 9 |
youtube.com
www.youtube.com — Cisco Umbrella Rank: 108 10yr old |
984 KB |
| 8 |
spotify.com
open.spotify.com — Cisco Umbrella Rank: 4374 10yr old apresolve.spotify.com — Cisco Umbrella Rank: 1448 9yr old gue1-spclient.spotify.com — Cisco Umbrella Rank: 2206 4yr old |
7 KB |
| 3 |
sentry.io
o22381.ingest.us.sentry.io — Cisco Umbrella Rank: 18704 2yr old |
412 B |
| 3 |
scdn.co
encore.scdn.co — Cisco Umbrella Rank: 7907 6yr old |
143 KB |
| 3 |
doubleclick.net
1 redirects
googleads.g.doubleclick.net — Cisco Umbrella Rank: 66 10yr old static.doubleclick.net — Cisco Umbrella Rank: 285 10yr old |
664 B |
| 3 |
googleapis.com
fonts.googleapis.com — Cisco Umbrella Rank: 43 10yr old jnn-pa.googleapis.com — Cisco Umbrella Rank: 343 5yr old |
1 KB |
| 2 |
gstatic.com
fonts.gstatic.com — Cisco Umbrella Rank: 29 10yr old |
71 KB |
| 1 |
ytimg.com
i.ytimg.com — Cisco Umbrella Rank: 124 10yr old |
37 KB |
| 1 |
google.com
www.google.com — Cisco Umbrella Rank: 3 14yr old |
24 KB |
| 73 | 11 |
| Domain | Requested by | |
|---|---|---|
| 20 | embed-cdn.spotifycdn.com |
open.spotify.com
embed-cdn.spotifycdn.com |
| 19 | godisaweapontour-com-github-io.pages.dev |
godisaweapontour-com-github-io.pages.dev
|
| 9 | www.youtube.com |
godisaweapontour-com-github-io.pages.dev
www.youtube.com |
| 5 | gue1-spclient.spotify.com |
embed-cdn.spotifycdn.com
|
| 3 | o22381.ingest.us.sentry.io |
embed-cdn.spotifycdn.com
|
| 3 | encore.scdn.co |
embed-cdn.spotifycdn.com
|
| 2 | jnn-pa.googleapis.com |
www.youtube.com
|
| 2 | apresolve.spotify.com |
embed-cdn.spotifycdn.com
|
| 2 | googleads.g.doubleclick.net |
1 redirects
www.youtube.com
|
| 2 | fonts.gstatic.com |
fonts.googleapis.com
www.youtube.com |
| 1 | i.ytimg.com |
www.youtube.com
|
| 1 | www.google.com |
www.youtube.com
|
| 1 | static.doubleclick.net |
www.youtube.com
|
| 1 | image-cdn-ak.spotifycdn.com |
open.spotify.com
|
| 1 | open.spotify.com |
godisaweapontour-com-github-io.pages.dev
|
| 1 | fonts.googleapis.com |
godisaweapontour-com-github-io.pages.dev
|
| 73 | 16 |
This site contains links to these domains. Also see Links.
| Domain |
|---|
| godisaweapontour.com |
| stubhub.prf.hn |
| facebook.com |
| instagram.com |
| x.com |
| www.youtube.com |
| www.spotify.com |
| Subject Issuer | Validity | Valid | |
|---|---|---|---|
| godisaweapontour-com-github-io.pages.dev WE1 |
2026-09-13 - 2026-12-12 |
3mo | crt.sh |
| upload.video.google.com WR2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| open.spotify.com Certainly Intermediate R1 |
2026-09-07 - 2026-10-07 |
1mo | crt.sh |
| *.google.com WE2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| *.gstatic.com WR2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| *.spotifycdn.com DigiCert Global G3 TLS ECC SHA384 2020 CA1 |
2026-07-01 - 2027-01-15 |
7mo | crt.sh |
| *.doubleclick.net WR2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| *.scdn.co DigiCert Global G3 TLS ECC SHA384 2020 CA1 |
2026-07-01 - 2027-01-15 |
7mo | crt.sh |
| ingest.sentry.io DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2026-08-06 - 2027-02-20 |
7mo | crt.sh |
| *.spotify.com DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2026-07-09 - 2027-01-23 |
7mo | crt.sh |
| edgestatic.com WR2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
This page contains 3 frames:
Primary Page:
https://godisaweapontour-com-github-io.pages.dev/
Frame ID: D75F1D8412301D86DDEF672F8E736F5E
Requests: 21 HTTP requests in this frame
Frame:
https://open.spotify.com/embed/artist/2CmaKO2zEGJ1NWpS1yfVGz
Frame ID: 9F7CBB7A2E2E6995639AE9EC9172A0BA
Requests: 35 HTTP requests in this frame
Frame:
https://www.youtube.com/embed/kc35iB4gIkw
Frame ID: 611151E71D5F8529D945354C0FEFC92D
Requests: 15 HTTP requests in this frame
Screenshot
Go Pro
Only in urlscan Pro
Use the Visual Search feature to find pages with visually similar screenshots.
Click for more information
Free trials of urlscan Pro are available.
Page Title
God Is a Weapon Tour : Falling In ReverseDetected technologies
 YouTube
(Video players)
Expand
Detected patterns
- <(?:param|embed|iframe)[^>]+youtube(?:-nocookie)?\.com/(?:v|embed)
- \.youtube\.com/
 DoubleClick Floodlight
(Advertising)
Expand
Detected patterns
- \.doubleclick\.net
HSTS (Security) Expand
Detected patterns
- ^https://[\w\d\.\-]+(?:\.dev)(?:/.+||/)$
 jQuery
(JavaScript libraries)
Expand
Detected patterns
- jquery
- /jquery(?:-(\d+\.\d+\.\d+))[/.-]
Page Statistics
8 Outgoing links
Go Pro
Only in urlscan Pro
Effortlessly use any on-page link as a pivot to discover other pages pointing to the exact same destination. Seamlessly trace both specific URLs and broader domains to uncover hidden connection networks and map out backlink relationships with ease.
Click for more information
Free trials of urlscan Pro are available.
These are links going to different origins than the main page.
Title: God Is a Weapon Tour
Search URL Search Domain Scan URL
Title: Buy Tickets
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Title: Privacy Policy
Search URL Search Domain Scan URL
Title: Terms & Conditions
Search URL Search Domain Scan URL
Redirected requests
There were HTTP redirect chains for the following requests:
Request Chain 43- https://googleads.g.doubleclick.net/pagead/id HTTP 302
- https://googleads.g.doubleclick.net/pagead/id?slf_rd=1
73 HTTP transactions
Go Pro
Only in urlscan Pro
Inspect WebSocket connections, examine POST data effortlessly, and track overlap counts in real time. Features live search and filtering across all HTTP output, complete with full response metadata for deep analysis.
Click for more information
Free trials of urlscan Pro are available.
0 data transactions
| Method Protocol |
Status | Resource Path |
Size x-fer |
Time Latency |
Type MIME-Type |
IP Location |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
|
GET H2 |
200 |
Primary Request
/
Show response
godisaweapontour-com-github-io.pages.dev/ |
12 KB 4 KB |
369ms
176ms |
Document
text/html |
172.66.44.152 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
reset.css
godisaweapontour-com-github-io.pages.dev/assets/css/ |
1 KB 908 B |
141ms
128ms |
Stylesheet
text/css |
172.66.44.152 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
swiper-bundle.min.css
godisaweapontour-com-github-io.pages.dev/assets/css/ |
13 KB 4 KB |
140ms
129ms |
Stylesheet
text/css |
172.66.44.152 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
styles.min.css
godisaweapontour-com-github-io.pages.dev/assets/css/ |
20 KB 5 KB |
140ms
129ms |
Stylesheet
text/css |
172.66.44.152 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
css2
fonts.googleapis.com/ |
4 KB 1 KB |
562ms
42ms |
Stylesheet
text/css |
142.251.167.95 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
main.jpg
godisaweapontour-com-github-io.pages.dev/assets/images/ |
97 KB 98 KB |
107ms
92ms |
Image
image/jpeg |
172.66.44.152 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
poster.jpg
godisaweapontour-com-github-io.pages.dev/assets/images/ |
646 KB 647 KB |
123ms
109ms |
Image
image/jpeg |
172.66.44.152 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
1.jpg
godisaweapontour-com-github-io.pages.dev/assets/images/gallery/ |
719 KB 720 KB |
151ms
135ms |
Image
image/jpeg |
172.66.44.152 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
2.jpg
godisaweapontour-com-github-io.pages.dev/assets/images/gallery/ |
597 KB 598 KB |
152ms
137ms |
Image
image/jpeg |
172.66.44.152 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
3.jpg
godisaweapontour-com-github-io.pages.dev/assets/images/gallery/ |
608 KB 609 KB |
171ms
160ms |
Image
image/jpeg |
172.66.44.152 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
4.jpg
godisaweapontour-com-github-io.pages.dev/assets/images/gallery/ |
465 KB 466 KB |
144ms
133ms |
Image
image/jpeg |
172.66.44.152 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
jquery-3.5.1.min.js
Show response
godisaweapontour-com-github-io.pages.dev/assets/js/ |
87 KB 32 KB |
181ms
167ms |
Script
application/javascript |
172.66.44.152 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
swiper-bundle.min.js
Show response
godisaweapontour-com-github-io.pages.dev/assets/js/ |
138 KB 37 KB |
144ms
131ms |
Script
application/javascript |
172.66.44.152 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
scripts.js
Show response
godisaweapontour-com-github-io.pages.dev/assets/js/ |
16 KB 5 KB |
121ms
108ms |
Script
application/javascript |
172.66.44.152 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
2CmaKO2zEGJ1NWpS1yfVGz
Show response
open.spotify.com/embed/artist/ Frame 9F7C |
25 KB 6 KB |
637ms
183ms |
Document
text/html |
151.101.3.42 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
kc35iB4gIkw
Show response
www.youtube.com/embed/ Frame 6111 |
151 KB 62 KB |
585ms
135ms |
Document
text/html |
142.251.151.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
L0x5DF4xlVMF-BfR8bXMIjhLq38.woff2
fonts.gstatic.com/s/robotomono/v31/ |
32 KB 32 KB |
403ms
51ms |
Font
font/woff2 |
172.253.62.94 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
fb-white.svg
godisaweapontour-com-github-io.pages.dev/assets/icons/ |
1 KB 999 B |
97ms
93ms |
Image
image/svg+xml |
172.66.44.152 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
inst-white.svg
godisaweapontour-com-github-io.pages.dev/assets/icons/ |
3 KB 1 KB |
132ms
127ms |
Image
image/svg+xml |
172.66.44.152 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
twitter-white.svg
godisaweapontour-com-github-io.pages.dev/assets/icons/ |
548 B 864 B |
149ms
144ms |
Image
image/svg+xml |
172.66.44.152 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
youtube-white.svg
godisaweapontour-com-github-io.pages.dev/assets/icons/ |
600 B 862 B |
129ms
125ms |
Image
image/svg+xml |
172.66.44.152 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
arrowdonw-white.svg
godisaweapontour-com-github-io.pages.dev/assets/icons/ |
372 B 774 B |
94ms
92ms |
Image
image/svg+xml |
172.66.44.152 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
www-player.css
www.youtube.com/s/player/8c3fda2d/ Frame 6111 |
531 KB 57 KB |
24ms
16ms |
Stylesheet
text/css |
142.251.151.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
m=root,base
www.youtube.com/s/_/ytembeds/_/ss/k=ytembeds.base.HY7wD9GGp-g.L.W.O/am=AAAAQA/d=1/br=1/rs=AGKMywE4Kjs9hFDhD74lwcLYIXdA_OMvQQ/ Frame 6111 |
0 438 B |
20ms
13ms |
Stylesheet
text/css |
142.251.151.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
m=root,base
Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywHdVJjs6ktwWXG8Pg3CpN4ZEVjBaQ/ Frame 6111 |
456 KB 155 KB |
29ms
23ms |
Script
text/javascript |
142.251.151.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
base.js
Show response
www.youtube.com/s/player/8c3fda2d/player_embed_es6_tcc.vflset/en_US/ Frame 6111 |
2 MB 473 KB |
46ms
40ms |
Script
text/javascript |
142.251.151.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
KFO7CnqEu92Fr1ME7kSn66aGLdTylUAMa3yUBA.woff2
fonts.gstatic.com/s/roboto/v48/ Frame 6111 |
39 KB 39 KB |
219ms
52ms |
Font
font/woff2 |
172.253.62.94 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
ae20dae031358b14.css
embed-cdn.spotifycdn.com/_next/static/css/ Frame 9F7C |
189 KB 25 KB |
345ms
72ms |
Stylesheet
text/css |
23.209.72.174 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
1392e34984c35024.css
embed-cdn.spotifycdn.com/_next/static/css/ Frame 9F7C |
35 KB 7 KB |
401ms
128ms |
Stylesheet
text/css |
23.209.72.174 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
b0f45d5f8a4235fd.css
embed-cdn.spotifycdn.com/_next/static/css/ Frame 9F7C |
18 KB 3 KB |
391ms
119ms |
Stylesheet
text/css |
23.209.72.174 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
webpack-f9046508ca8c51da.js
Show response
embed-cdn.spotifycdn.com/_next/static/chunks/ Frame 9F7C |
6 KB 3 KB |
356ms
91ms |
Script
text/javascript |
23.209.72.174 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
framework-6f473f6ede4ec4c4.js
Show response
embed-cdn.spotifycdn.com/_next/static/chunks/ Frame 9F7C |
186 KB 59 KB |
434ms
170ms |
Script
text/javascript |
23.209.72.174 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
main-05f830001ca4cc3e.js
Show response
embed-cdn.spotifycdn.com/_next/static/chunks/ Frame 9F7C |
137 KB 41 KB |
342ms
77ms |
Script
text/javascript |
23.209.72.174 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
_app-2889172452a7bb94.js
Show response
embed-cdn.spotifycdn.com/_next/static/chunks/pages/ Frame 9F7C |
387 KB 123 KB |
83ms
79ms |
Script
text/javascript |
23.209.72.174 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
69bd4b51-865e1672b6809701.js
Show response
embed-cdn.spotifycdn.com/_next/static/chunks/ Frame 9F7C |
318 KB 99 KB |
100ms
96ms |
Script
text/javascript |
23.209.72.174 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
1df930d7-c3c84ee0b3e2843b.js
Show response
embed-cdn.spotifycdn.com/_next/static/chunks/ Frame 9F7C |
9 KB 2 KB |
95ms
92ms |
Script
text/javascript |
23.209.72.174 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
8494-228b98ef7673b262.js
Show response
embed-cdn.spotifycdn.com/_next/static/chunks/ Frame 9F7C |
10 KB 4 KB |
64ms
61ms |
Script
text/javascript |
23.209.72.174 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
4504-10c402f02bc5b2f3.js
Show response
embed-cdn.spotifycdn.com/_next/static/chunks/ Frame 9F7C |
416 KB 125 KB |
89ms
86ms |
Script
text/javascript |
23.209.72.174 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
7544-5f0256793a2ea960.js
Show response
embed-cdn.spotifycdn.com/_next/static/chunks/ Frame 9F7C |
136 KB 40 KB |
104ms
102ms |
Script
text/javascript |
23.209.72.174 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
4473-0584bcaf9a8aef0d.js
Show response
embed-cdn.spotifycdn.com/_next/static/chunks/ Frame 9F7C |
21 KB 7 KB |
63ms
61ms |
Script
text/javascript |
23.209.72.174 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
%5Bid%5D-f33ebb31fa43927d.js
Show response
embed-cdn.spotifycdn.com/_next/static/chunks/pages/artist/ Frame 9F7C |
1 KB 1 KB |
65ms
63ms |
Script
text/javascript |
23.209.72.174 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
_buildManifest.js
Show response
embed-cdn.spotifycdn.com/_next/static/067fedce-c95d-4edb-9893-24dc16539ce3/ Frame 9F7C |
3 KB 1 KB |
86ms
84ms |
Script
text/javascript |
23.209.72.174 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
_ssgManifest.js
Show response
embed-cdn.spotifycdn.com/_next/static/067fedce-c95d-4edb-9893-24dc16539ce3/ Frame 9F7C |
77 B 405 B |
71ms
69ms |
Script
text/javascript |
23.209.72.174 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
ab6761610000f1784a733f510df96652c3bea05b
image-cdn-ak.spotifycdn.com/image/ Frame 9F7C |
7 KB 7 KB |
295ms
25ms |
Image
image/jpeg |
23.219.161.116 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
id
Show response
googleads.g.doubleclick.net/pagead/ Frame 6111 Redirect Chain
|
100 B 146 B |
41ms
40ms |
XHR
application/json |
142.250.31.156 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
ad_status.js
Show response
static.doubleclick.net/instream/ Frame 6111 |
29 B 495 B |
261ms
28ms |
Script
text/javascript |
142.251.163.149 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
m=r78Drb
Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/ck=ytembeds.base.HY7wD9GGp-g.L.W.O/am=AAAAQA/d=1/exm=base,root/excm=base,root/ed=1/br=1/rs=AGKMywEii8DElVVeiaz1NP5LoXHZcDQ... Frame 6111 |
906 KB 219 KB |
21ms
18ms |
Script
text/javascript |
142.251.151.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
SpotifyMixUI-Regular-76c92fb1a35c462f73429fa8865163eb.woff2
encore.scdn.co/fonts/ Frame 9F7C |
43 KB 44 KB |
181ms
34ms |
Font
font/woff |
23.193.201.53 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
SpotifyMixUI-Bold-09c45a3a0ce9d2971e62cb26e97760fb.woff2
encore.scdn.co/fonts/ Frame 9F7C |
46 KB 47 KB |
180ms
33ms |
Font
font/woff |
23.193.201.53 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
Nnzuu5J_F_O4BdIqIrU2lZhdT-H-buEFYIxLjbvxu_0.js
Show response
www.google.com/js/th/ Frame 6111 |
62 KB 24 KB |
49ms
15ms |
Script
text/javascript |
142.251.151.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
d6cd3fda-86e3-423c-b8aa-3ccf01d79fc1
https://open.spotify.com/ Frame 9F7C |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
/
Show response
o22381.ingest.us.sentry.io/api/4505164808585216/envelope/ Frame 9F7C |
2 B 300 B |
560ms
33ms |
Fetch
application/json |
34.160.81.0 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
/
Show response
o22381.ingest.us.sentry.io/api/4505164808585216/envelope/ Frame 9F7C |
2 B 56 B |
89ms
37ms |
Fetch
application/json |
34.160.81.0 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
/
Show response
o22381.ingest.us.sentry.io/api/4505164808585216/envelope/ Frame 9F7C |
2 B 56 B |
42ms
31ms |
Fetch
application/json |
34.160.81.0 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
/
Show response
apresolve.spotify.com/ Frame 9F7C |
288 B 336 B |
405ms
60ms |
XHR
application/json |
35.186.224.24 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
m=cwx9N
Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/ck=ytembeds.base.HY7wD9GGp-g.L.W.O/am=AAAAQA/d=1/exm=base,r78Drb,root/excm=base,root/ed=1/br=1/rs=AGKMywEii8DElVVeiaz1NP5L... Frame 6111 |
66 KB 17 KB |
22ms
21ms |
Script
text/javascript |
142.251.151.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
/
Show response
apresolve.spotify.com/ Frame 9F7C |
288 B 170 B |
404ms
125ms |
Fetch
application/json |
35.186.224.24 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
da236039.77ef9cc158887e7e.js
Show response
embed-cdn.spotifycdn.com/_next/static/chunks/ Frame 9F7C |
62 KB 16 KB |
32ms
28ms |
Script
text/javascript |
23.209.72.174 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
5039.a54f1bd47316601a.js
Show response
embed-cdn.spotifycdn.com/_next/static/chunks/ Frame 9F7C |
47 KB 12 KB |
35ms
32ms |
Script
text/javascript |
23.209.72.174 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
8272.358f99da4dbaadef.js
Show response
embed-cdn.spotifycdn.com/_next/static/chunks/ Frame 9F7C |
341 KB 86 KB |
41ms
39ms |
Script
text/javascript |
23.209.72.174 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
spotify_player_o.fb37a86507bf6388.js
Show response
embed-cdn.spotifycdn.com/_next/static/chunks/ Frame 9F7C |
12 KB 5 KB |
27ms
25ms |
Script
text/javascript |
23.209.72.174 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
maxresdefault.jpg
i.ytimg.com/vi/kc35iB4gIkw/ Frame 6111 |
37 KB 37 KB |
366ms
193ms |
Image
image/jpeg |
142.251.167.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
SpotifyMixUITitle-Bold-2c79abf9c6697da8b2bf5af3f11e6913.woff2
encore.scdn.co/fonts/ Frame 9F7C |
52 KB 52 KB |
52ms
21ms |
Font
font/woff |
23.193.201.53 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
204 |
generate_204
www.youtube.com/ Frame 6111 |
0 10 B |
34ms
19ms |
Image
text/plain |
142.251.151.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
events
Show response
gue1-spclient.spotify.com/gabo-receiver-service/public/v3/ Frame 9F7C |
13 B 164 B |
73ms
71ms |
Fetch
application/json |
35.186.224.9 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
OPTIONS H2 |
200 |
events
gue1-spclient.spotify.com/gabo-receiver-service/public/v3/ Frame |
0 0 |
138ms
56ms |
Preflight
|
35.186.224.9 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
GenerateIT
Show response
jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/ Frame 6111 |
94 B 304 B |
57ms
54ms |
XHR
application/json+protobuf |
172.217.116.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
OPTIONS H2 |
200 |
GenerateIT
jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/ Frame |
0 0 |
96ms
51ms |
Preflight
text/html |
172.217.116.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
favicon.ico
godisaweapontour-com-github-io.pages.dev/ |
15 KB 4 KB |
153ms
149ms |
Other
image/vnd.microsoft.icon |
172.66.44.152 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
200 |
events
Show response
gue1-spclient.spotify.com/gabo-receiver-service/public/v3/ Frame 9F7C |
13 B 32 B |
80ms
79ms |
Fetch
application/json |
35.186.224.9 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
200 |
log_event
Show response
www.youtube.com/youtubei/v1/ Frame 6111 |
28 B 50 B |
49ms
44ms |
XHR
application/json |
142.251.151.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
200 |
events
Show response
gue1-spclient.spotify.com/gabo-receiver-service/public/v3/ Frame 9F7C |
13 B 32 B |
92ms
90ms |
XHR
application/json |
35.186.224.9 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
200 |
events
Show response
gue1-spclient.spotify.com/gabo-receiver-service/public/v3/ Frame 9F7C |
13 B 32 B |
98ms
97ms |
XHR
application/json |
35.186.224.9 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||




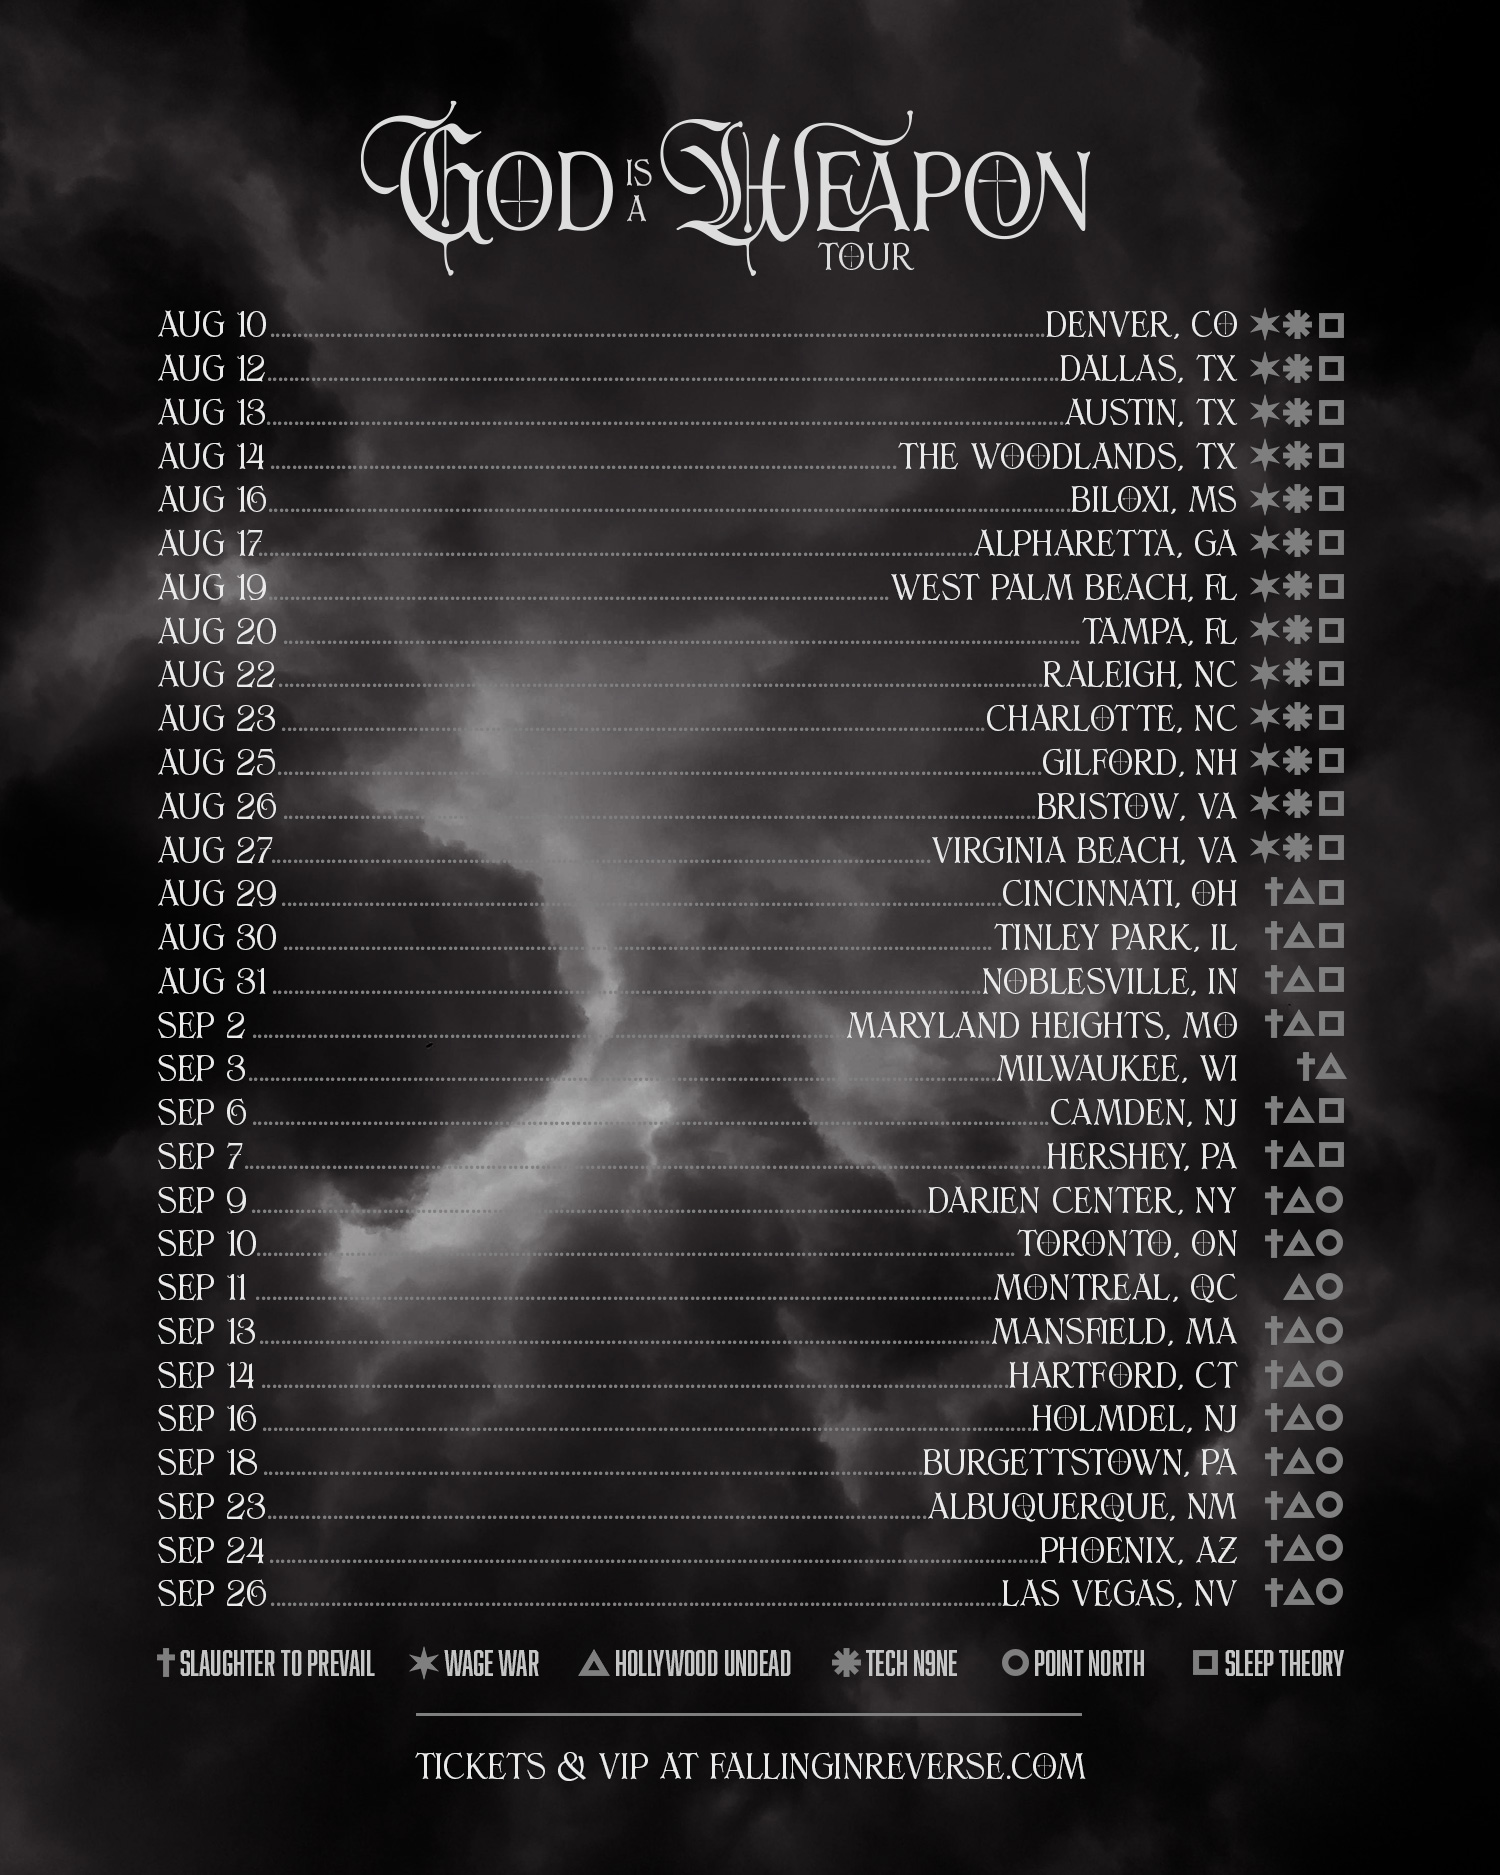










Failed requests
These URLs were requested, but there was no response received. You will also see them in the list above.
- Domain
- open.spotify.com
- URL
- blob:https://open.spotify.com/d6cd3fda-86e3-423c-b8aa-3ccf01d79fc1
Verdicts & Comments Add Verdict or Comment
11 JavaScript Window variables
Go Pro
Only in urlscan Pro
Inspect and pivot on JavaScript variables, identifiers, and other key site metadata data with urlscan Pro. Reveal and search on client-side frameworks, runtime variables, and custom values.
Click for more information
Free trials of urlscan Pro are available.
These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.
object| 0 object| 1 function| $ function| jQuery function| Swiper string| reviews_title function| moveSlider function| currentSlide function| toggleFullscreen function| moveFullscreenSlider function| currentFullscreenSlide7 Cookies
Go Pro
Only in urlscan Pro
Review, search, and pivot on browser cookies and persistence site data to see how a site tracks users and keeps sessions alive across visits.
Click for more information
Free trials of urlscan Pro are available.
Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.
| Domain/Path | Expires | Name / Value | |||
|---|---|---|---|---|---|
| .youtube.com/ | 1970-01-21 21:20:21 |
Name: __Secure-YNID Value: 21.YT=g0Ew7EzZj0eFEI9wfN-d5AcxCohIYsRmmMVwa0nwlyrVIW10w_am5SQV7gd53nsd2rwEnUQbpVh03mwuxTa0elcEXDX7fEtuReQD0Ik0-lIXWaxfP4b0RTOX7gafwMuPhPoCtnbdciZ1H4FcPynAUgl5PbdZ3KDwHi3-RWES_l0Bi4H3GIMqzP8fjcQ0qWvOP3XD9GO7J-yJoqIHN71skw_iTDGsqUKSRQPG37OCdX8PvTGP_8bI1DAEnC4jKhiyKbXmstg7gGMoj-KMxAo1hkp-CmA6EcvF--DbvEUe9DFOQQaRbc-WakCa_VRcnQy9ktcnmyUOdZiLs_4JG9l53w |
|||
| .youtube.com/ | 1969-12-31 23:59:59 |
Name: YSC Value: ZwA55IB2AYo |
|||
| .youtube.com/ | 1970-01-21 21:20:21 |
Name: VISITOR_INFO1_LIVE Value: FAvqPnJQK2Y |
|||
| .youtube.com/ | 1970-01-21 21:20:21 |
Name: VISITOR_PRIVACY_METADATA Value: CgJDQRIEGgAgbA%3D%3D |
|||
| .youtube.com/ | 1970-01-21 21:20:21 |
Name: __Secure-ROLLOUT_TOKEN Value: CNe9ncGI08ur8wEQtLLqncvqlgMYtLLqncvqlgM%3D |
|||
| .spotify.com/ | 1970-01-22 01:46:45 |
Name: sp_t Value: e8d66013e9fbac7e3edc2f62e2c34938 |
|||
| .spotify.com/ | 1970-01-21 17:02:35 |
Name: sp_landing Value: https%3A%2F%2Fgodisaweapontour-com-github-io.pages.dev%2F%3Fsp_cid%3De8d66013e9fbac7e3edc2f62e2c34938%26device%3Ddesktop |
31 Console Messages
A page may trigger messages to the console to be logged. These are often error messages about being unable to load a resource or execute a piece of JavaScript. Sometimes they also provide insight into the technology behind a website.
| Source | Level | URL Text |
|---|
Security Headers
This page lists any security headers set by the main page. If you want to understand what these mean and how to use them, head on over to this page
| Header | Value |
|---|---|
| X-Content-Type-Options | nosniff |
Indicators
This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.
apresolve.spotify.com
embed-cdn.spotifycdn.com
encore.scdn.co
fonts.googleapis.com
fonts.gstatic.com
godisaweapontour-com-github-io.pages.dev
googleads.g.doubleclick.net
gue1-spclient.spotify.com
i.ytimg.com
image-cdn-ak.spotifycdn.com
jnn-pa.googleapis.com
o22381.ingest.us.sentry.io
open.spotify.com
static.doubleclick.net
www.google.com
www.youtube.com
open.spotify.com
142.250.31.156
142.251.151.119
142.251.151.4
142.251.163.149
142.251.167.119
142.251.167.95
151.101.3.42
172.217.116.4
172.253.62.94
172.66.44.152
23.193.201.53
23.209.72.174
23.219.161.116
34.160.81.0
35.186.224.24
35.186.224.9
0184cc3dd35f6dfe627898fcd0a885fcd8f2be87e3b7a9174db56d1165605d60
06b6bfd701935f12f5a4da30cf760cf8c56801784610b0e07abb7f9cc1f0fd9c
0bf84095f5f86af844a2f90242d28eddd2f2f6f1b61584dfb9edde5056a57008
0e1c4e6a0fd2f5fd72f6a8d19fdcf0f37190b79396485c324e95891a135a1b0a
1af0c9502f8b13f9bc24b6ba1cd1f5313903dd0209a3dccdad8ea5b26998de49
1e6f131e5c23998532caa01dec741cd746efdb7364cffaf33a43f227aaa0d458
20b535fa80c8189e3b87d1803038389960203a886d502bc2ef1857affc2f38d2
2aa16a26180b4df3991393ccd09149de21dc75a65ba9e23baf41d8f14bb9d978
2b2abb5c8629afda1fa8c14d84c9070e3361d5bc48170498e85387c3f1044961
2be51c30dcafc8fadbb19d36d229feb3678dab7cc0a9cdcd69361da90b491728
2cf09eafc0a88653442cd856390ab34b85a30110304d23a23071c183547732af
2d0507a3f4015bcc7d735092ae2b81978f6b618b8beb3e4fbdf7c61b1e832f55
2ddc0b6b42ab9583ac8d119f0c0c42db5d9500a1ee4d8245e09fedc6d6b85726
2f59f0d2855e47e3127ea576df1a6d432564490b6c16104fbdff11f2f150cd71
367ceebb927f17f3b805d22a22b53695985d4fe1fe6ee105608c4b8dbbf1bbfd
3d17c118c0e31d29647bbafcb997f4e00de59cbd6f2287e9e70e42ec471879b2
44136fa355b3678a1146ad16f7e8649e94fb4fc21fe77e8310c060f61caaff8a
48375d95059d5dba1f2a39c9f93cc0be34f760d9cf55d284bc3bcbc442e8a784
51b9b3a69c279187da1c3108889c998f6aafa0d59457e3b7990220b17598fcd4
555e95e5af65cfd867790ac83d0f93780e6a63078135648b21c4fb935c1e04b0
5d62ff681907891c23a4da240ee06c35319160a317359cf4aed53eb40b4ea5e2
64dff2e81de9d88a4a37d05aef98f4ca8220b25c85b00d52077e6d99bd0a651a
676e1bb90919ec2910a0bf940c6345e9e969475102fe355a98ded10627a20152
6f5b4aa00d2f8d6aed9935b471806bf7acef464d0c1d390260e5fe27f800c67e
75cfd90ada8cba0dde0d7a217878481038e3efec2fb98b7789a2180b27b51eb9
78a27218d5a159bc9d4507d974580d7c9ba564902e45981fde1241db614f0952
7ae1e10427cfe267b8111005222daba20d807bb2a78cc53b7788e7ec6247e2d0
7c3e364986be1d184bdc051d0fab5c95e52161e3f0e80374cf2e3116c500d828
8629be6cc3e10ce33c4fabb9c9dfb1343affc91b21d13f26fe2c48663f631f8d
869d5074adafd2eb974065b552e2d6b490be776488c5a937890059a04db7342b
86b742cfa596799c1a5856ba629afdd7b7b1e5478112bbb2101d126b9a2c75d9
8717aeff3abcfd3b9034940ad18c214085ab130900888f34b58dfc74897c3e5c
8dbfcb50e8aef721bd00b06f5874a94b8f88008c7dd432691ff405158bf8b080
97b075424653a2f0b3b905f1110dc49c6cf67c1a1d26b4bf6f87a6ca52556ba0
99979ddf7eaa30cb8975284533174b8006ee13d38881192308bbd00eca52cfac
9a2723c21fb1b7dff0e2aa5dc6be24a9670220a17ae21f70fdbc602d1f8acd38
9a6f174d593d8404d55c3ba5b8ddc199d63196b87c1cf40b061fe0266660af3d
9aa3fd4d18c32fa290cd2edb49bd7a72d59d39b3037aa1c3a876bc034e7a055d
9d66ed39cd90111abe8be07798b65f01076983dcead837eada3c68219e1cd383
a35ce74f2794876945ceee84fb3ec25273d51919405c018475981d446d8b529f
a45b6c51281f47d17a1743bd115a6ac729336f86fd16a420a3d2d4bb92d849c3
a58d10c7b14749a557b7fd2ce4bf12e5f776c6f32ae194bbdb5c3c5898f0dc61
b1e2649bec302deb150e30cc9d1edb32a426b96dcc6c2669abde29cd787111a0
b4aa122860b114c33243cac52bdb8d7a7454892ad77646995880986c70c03d51
b5e1a223f118cf9ffbb6c79ff14792684360f910fc47e07c8c5f3246e9d3709d
b5eb9c20d89c1077349b5b4381a3fe3a914793e0f0c2ead42a2b2d9686af2665
b81cd55177300649be8f95b3b747d721ce607e8ed2856e25bd0c630cfd631faf
c7a10d416879f92e668be303b13fd74c83276edf158943d5e5e8a991a7fee5b0
c8a4591268a58564b71512a5a52cae0029a67d44f87ebd030af05ef7e6339d49
c97b2f455faddf0b4f7addc3375f83eb2d20e81069ef77647130cc995b0f87bd
c997073a2f4d56aa6dcc7677d21134c14f7e36ac614091c2f27ad50a8c1fb534
d46d3354002b8d2b611c4daca991368e8e6fefcbb8938770f04cf5aa965fa4fb
d7d5e54ad1e33d7ab49c664323ced79cb9723ff15e9764cd0edc3e15208e8336
de6ac9dc9a7d6a896fc131c1184a8f53d86cc38a523ccc83588d4dbb80c8a498
debf84af8d66827e1cbc6791aa686504e3116d8cb20f4697fef23108333061f8
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
e3f3f1d2593aa2d8771033736d5be7d807e450284abb2ed55fa55c937a197cc7
eed0dc1fdb5d97ed188ae16fd5e1024a5bb744af47340346be2146300a6c54b9
ef38823b213ea9b5ff92713325518da04cc69aae9e17de60c2f0eb739c21976a
f0f5a8c3af9b73ef4683a410e589fc451df61a250307b7f0e1d5c61881afd2df
f115f4cf012d4a1ae1f4e075698752893b63cf0e64035f1899f2b36f89fa46dc
f16921bfc321f15355bee74386deaa8921dc0272a2adeaf05d377e7402b76d39
f87d595a0c03526dfd6fbe286f10aa64db86a41c4ca59489ba659fc318e3a514
f9d8ab207f92c089ccbdbaae5a5e813194f2e06e33ac39b5adc896a67a10ffcd