
www.contactazanix.com
157.53.227.1
Public Scan
Open in
urlscan Pro
https://www.contactazanix.com/ 1yr old
Submission: On September 13 via automatic, source certstream-suspicious (September 13th 2026, 5:01:15 am UTC) — Scanned from CA Go Pro
Only in urlscan Pro
- Select different country locations for Private Scans.
- Use a global network of additional scanning locations and residential IPs for scanning.
- Interact with pages while you are scanning them.
- Download files from remote websites.
- Scan websites on the Tor Network.
Summary
TLS certificate: Issued by YR2 on June 29th 2026. Valid for: 3mo.
This is the only time www.contactazanix.com was scanned on urlscan.io!
urlscan.io Verdict: No classification
Domain & IP information
| IP Address | AS Autonomous System | ||
|---|---|---|---|
| 2 | 157.53.227.1 157.53.227.1 | 63911 (NETACTUAT...) (NETACTUATE-AS-AP - NetActuate) | |
| 1 | 151.101.193.55 151.101.193.55 | 54113 (FASTLY) (FASTLY - Fastly) | |
| 2 | 99.84.160.9 99.84.160.9 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 4 | 151.101.2.132 151.101.2.132 | 54113 (FASTLY) (FASTLY - Fastly) | |
| 8 | 172.67.73.53 172.67.73.53 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 4 | 142.251.167.95 142.251.167.95 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 13.33.252.127 13.33.252.127 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 6 | 13.32.241.17 13.32.241.17 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 1 | 104.18.11.207 104.18.11.207 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 3.171.117.19 3.171.117.19 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 5 | 172.253.62.94 172.253.62.94 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 3.168.102.124 3.168.102.124 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 1 | 52.85.61.87 52.85.61.87 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 1 | 3.5.69.57 3.5.69.57 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 1 | 142.251.152.119 142.251.152.119 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 2 | 142.250.217.3 142.250.217.3 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 3 | 142.251.154.119 142.251.154.119 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 45 | 18 |
ASN63911 (NETACTUATE-AS-AP - NetActuate, Inc, US)
PTR: 1.227.53.157.ptr.anycast.net
| www.contactazanix.com 1yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-99-84-160-9.jfk50.r.cloudfront.net
| assetslp.link 4yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| images.assets-landingi.com 9yr old | |
| styles.assets-landingi.com 9yr old | |
| scripts.assets-landingi.com 9yr old | |
| old.assets-landingi.com 9yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: ww-in-f95.1e100.net
| fonts.googleapis.com 10yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-13-33-252-127.jfk50.r.cloudfront.net
| popups.landingi.com 7yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-13-32-241-17.jfk50.r.cloudfront.net
| icons.assets-landingi.com 4yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| maxcdn.bootstrapcdn.com 10yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-3-171-117-19.jfk50.r.cloudfront.net
| tagmanager.landingi.io 4yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: bc-in-f94.1e100.net
| fonts.gstatic.com 10yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-3-168-102-124.jfk52.r.cloudfront.net
| stats.landingi.com 7yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-52-85-61-87.ewr53.r.cloudfront.net
| lightboxes.landingi.com 6yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
| s3.eu-west-1.amazonaws.com 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: pnlgaa-as-in-f3.1e100.net
| www.gstatic.com 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
| www.google.com 14yr old | |
| www.gstatic.com 10yr old |
| Apex Domain Subdomains |
Transfer | |
|---|---|---|
| 14 |
assets-landingi.com
images.assets-landingi.com — Cisco Umbrella Rank: 264277 9yr old styles.assets-landingi.com — Cisco Umbrella Rank: 250894 9yr old scripts.assets-landingi.com — Cisco Umbrella Rank: 229338 9yr old icons.assets-landingi.com — Cisco Umbrella Rank: 278127 4yr old old.assets-landingi.com — Cisco Umbrella Rank: 279160 9yr old |
153 KB |
| 9 |
gstatic.com
fonts.gstatic.com — Cisco Umbrella Rank: 29 10yr old www.gstatic.com — Cisco Umbrella Rank: 8 10yr old |
579 KB |
| 4 |
googleapis.com
fonts.googleapis.com — Cisco Umbrella Rank: 43 10yr old |
6 KB |
| 4 |
lugc.link
cdn.lugc.link — Cisco Umbrella Rank: 254184 6yr old |
99 KB |
| 3 |
landingi.com
popups.landingi.com — Cisco Umbrella Rank: 205434 7yr old stats.landingi.com — Cisco Umbrella Rank: 238989 7yr old lightboxes.landingi.com — Cisco Umbrella Rank: 275764 6yr old |
7 KB |
| 2 |
google.com
www.google.com — Cisco Umbrella Rank: 3 14yr old |
29 KB |
| 2 |
assetslp.link
assetslp.link — Cisco Umbrella Rank: 265985 4yr old |
35 KB |
| 2 |
contactazanix.com
www.contactazanix.com 1yr old |
21 KB |
| 1 |
amazonaws.com
s3.eu-west-1.amazonaws.com 10yr old |
5 KB |
| 1 |
landingi.io
tagmanager.landingi.io — Cisco Umbrella Rank: 268349 4yr old |
2 KB |
| 1 |
bootstrapcdn.com
maxcdn.bootstrapcdn.com — Cisco Umbrella Rank: 1473 10yr old |
6 KB |
| 1 |
ucarecdn.com
ucarecdn.com — Cisco Umbrella Rank: 19855 14yr old |
8 KB |
| 45 | 12 |
| Domain | Requested by | |
|---|---|---|
| 6 | icons.assets-landingi.com |
www.contactazanix.com
styles.assets-landingi.com |
| 5 | fonts.gstatic.com |
fonts.googleapis.com
www.google.com |
| 4 | www.gstatic.com |
www.google.com
www.gstatic.com |
| 4 | fonts.googleapis.com |
www.contactazanix.com
scripts.assets-landingi.com |
| 4 | cdn.lugc.link |
www.contactazanix.com
|
| 3 | scripts.assets-landingi.com |
www.contactazanix.com
|
| 3 | styles.assets-landingi.com |
www.contactazanix.com
scripts.assets-landingi.com |
| 2 | www.google.com |
assetslp.link
www.gstatic.com |
| 2 | assetslp.link |
www.contactazanix.com
|
| 2 | www.contactazanix.com |
www.contactazanix.com
|
| 1 | s3.eu-west-1.amazonaws.com | |
| 1 | lightboxes.landingi.com |
scripts.assets-landingi.com
|
| 1 | stats.landingi.com |
www.contactazanix.com
|
| 1 | tagmanager.landingi.io |
www.contactazanix.com
|
| 1 | maxcdn.bootstrapcdn.com |
www.contactazanix.com
|
| 1 | old.assets-landingi.com |
www.contactazanix.com
|
| 1 | popups.landingi.com |
www.contactazanix.com
|
| 1 | images.assets-landingi.com |
www.contactazanix.com
|
| 1 | ucarecdn.com |
www.contactazanix.com
|
| 45 | 19 |
This site contains no links.
| Subject Issuer | Validity | Valid | |
|---|---|---|---|
| www.contactazanix.com YR2 |
2026-06-29 - 2026-09-27 |
3mo | crt.sh |
| ucarecdn.com Certainly Intermediate R1 |
2026-09-06 - 2026-10-06 |
1mo | crt.sh |
| assetslp.link Amazon RSA 2048 M04 |
2026-08-14 - 2027-02-27 |
7mo | crt.sh |
| cdn.lugc.link Certainly Intermediate R1 |
2026-08-24 - 2026-09-23 |
1mo | crt.sh |
| assets-landingi.com WE1 |
2026-08-08 - 2026-11-06 |
3mo | crt.sh |
| upload.video.google.com WR2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| landingi.com Amazon RSA 2048 M01 |
2026-05-20 - 2026-12-03 |
7mo | crt.sh |
| bootstrapcdn.com WE1 |
2026-08-29 - 2026-11-27 |
3mo | crt.sh |
| tagmanager.landingi.io Amazon RSA 2048 M01 |
2026-05-01 - 2026-11-14 |
7mo | crt.sh |
| *.gstatic.com WR2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| *.s3-eu-west-1.amazonaws.com Amazon RSA 2048 M04 |
2025-11-14 - 2026-11-06 |
1yr | crt.sh |
| *.google.com WE2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
This page contains 2 frames:
Primary Page:
https://www.contactazanix.com/
Frame ID: 54FC1AD5AF4315B0EAF5C7EB08DB2579
Requests: 39 HTTP requests in this frame
Frame:
https://www.google.com/recaptcha/api2/anchor?ar=1&k=6LdKrHsjAAAAABdQ3WpMFH24cXPVkm1YA-KQWjW-&co=aHR0cHM6Ly93d3cuY29udGFjdGF6YW5peC5jb206NDQz&hl=en&v=BnqMGSY_YP4cCmbNINHpJPkd&size=invisible&anchor-ms=20000&execute-ms=30000&cb=q57usqs1zc6y
Frame ID: 04337AADDF4BA7121D3FA5BDF75BE34B
Requests: 6 HTTP requests in this frame
Screenshot
Go Pro
Only in urlscan Pro
Use the Visual Search feature to find pages with visually similar screenshots.
Click for more information
Free trials of urlscan Pro are available.
Page Title
Azanix ConsultingDetected technologies
 Landingi
(Page builders)
Expand
Detected patterns
- scripts\.assets-landingi\.com
 Amazon S3
(CDN)
Expand
Detected patterns
- s3[^ ]*\.amazonaws\.com/
 Font Awesome
(Font scripts)
Expand
Detected patterns
- (?:F|f)o(?:n|r)t-?(?:A|a)wesome(?:.*?([0-9a-fA-F]{7,40}|[\d]+(?:.[\d]+(?:.[\d]+)?)?)|)
 jQuery
(JavaScript libraries)
Expand
Detected patterns
- jquery
 Lightbox
(JavaScript libraries)
Expand
Detected patterns
- lightbox(?:-plus-jquery)?.{0,32}\.js
 reCAPTCHA
(Security)
Expand
Detected patterns
- /recaptcha/(?:api|enterprise)\.js
Page Statistics
0 Outgoing links
Go Pro
Only in urlscan Pro
Effortlessly use any on-page link as a pivot to discover other pages pointing to the exact same destination. Seamlessly trace both specific URLs and broader domains to uncover hidden connection networks and map out backlink relationships with ease.
Click for more information
Free trials of urlscan Pro are available.
These are links going to different origins than the main page.
Redirected requests
There were HTTP redirect chains for the following requests:
45 HTTP transactions
Go Pro
Only in urlscan Pro
Inspect WebSocket connections, examine POST data effortlessly, and track overlap counts in real time. Features live search and filtering across all HTTP output, complete with full response metadata for deep analysis.
Click for more information
Free trials of urlscan Pro are available.
0 data transactions
| Method Protocol |
Status | Resource Path |
Size x-fer |
Time Latency |
Type MIME-Type |
IP Location |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
|
GET H2 |
200 |
Primary Request
/
Show response
www.contactazanix.com/ |
29 KB 9 KB |
754ms
656ms |
Document
text/html |
157.53.227.1 NetActuate |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
frodo.js
Show response
www.contactazanix.com/assets/js/landend/ |
30 KB 11 KB |
61ms
25ms |
Script
application/javascript |
157.53.227.1 NetActuate |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
blinkloader.min.js
Show response
ucarecdn.com/libs/blinkloader/3.x/ |
8 KB 8 KB |
97ms
11ms |
Script
application/javascript |
151.101.193.55 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
lazysizes.min.js
Show response
assetslp.link/assets/js/landend/ |
10 KB 5 KB |
114ms
25ms |
Script
application/javascript |
99.84.160.9 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
/
cdn.lugc.link/dc586a01-e673-447c-a41f-2c460e9595ab/-/stretch/off/-/resize/1800x/-/format/auto/ |
51 KB 51 KB |
126ms
40ms |
Image
image/avif |
151.101.2.132 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
/
cdn.lugc.link/d1d7841b-fa18-4ffb-870f-cf3fe5df790e/-/stretch/off/-/resize/x243/-/format/auto/ |
11 KB 11 KB |
96ms
11ms |
Image
image/avif |
151.101.2.132 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
/
cdn.lugc.link/b65cced1-678a-412e-99e8-5fb910894b84/-/stretch/off/-/resize/x243/-/format/auto/ |
12 KB 12 KB |
98ms
14ms |
Image
image/avif |
151.101.2.132 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
/
cdn.lugc.link/8862e5a7-4469-4cd2-878f-9ffbc86750af/-/stretch/off/-/resize/x494/-/format/auto/ |
24 KB 24 KB |
97ms
13ms |
Image
image/avif |
151.101.2.132 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
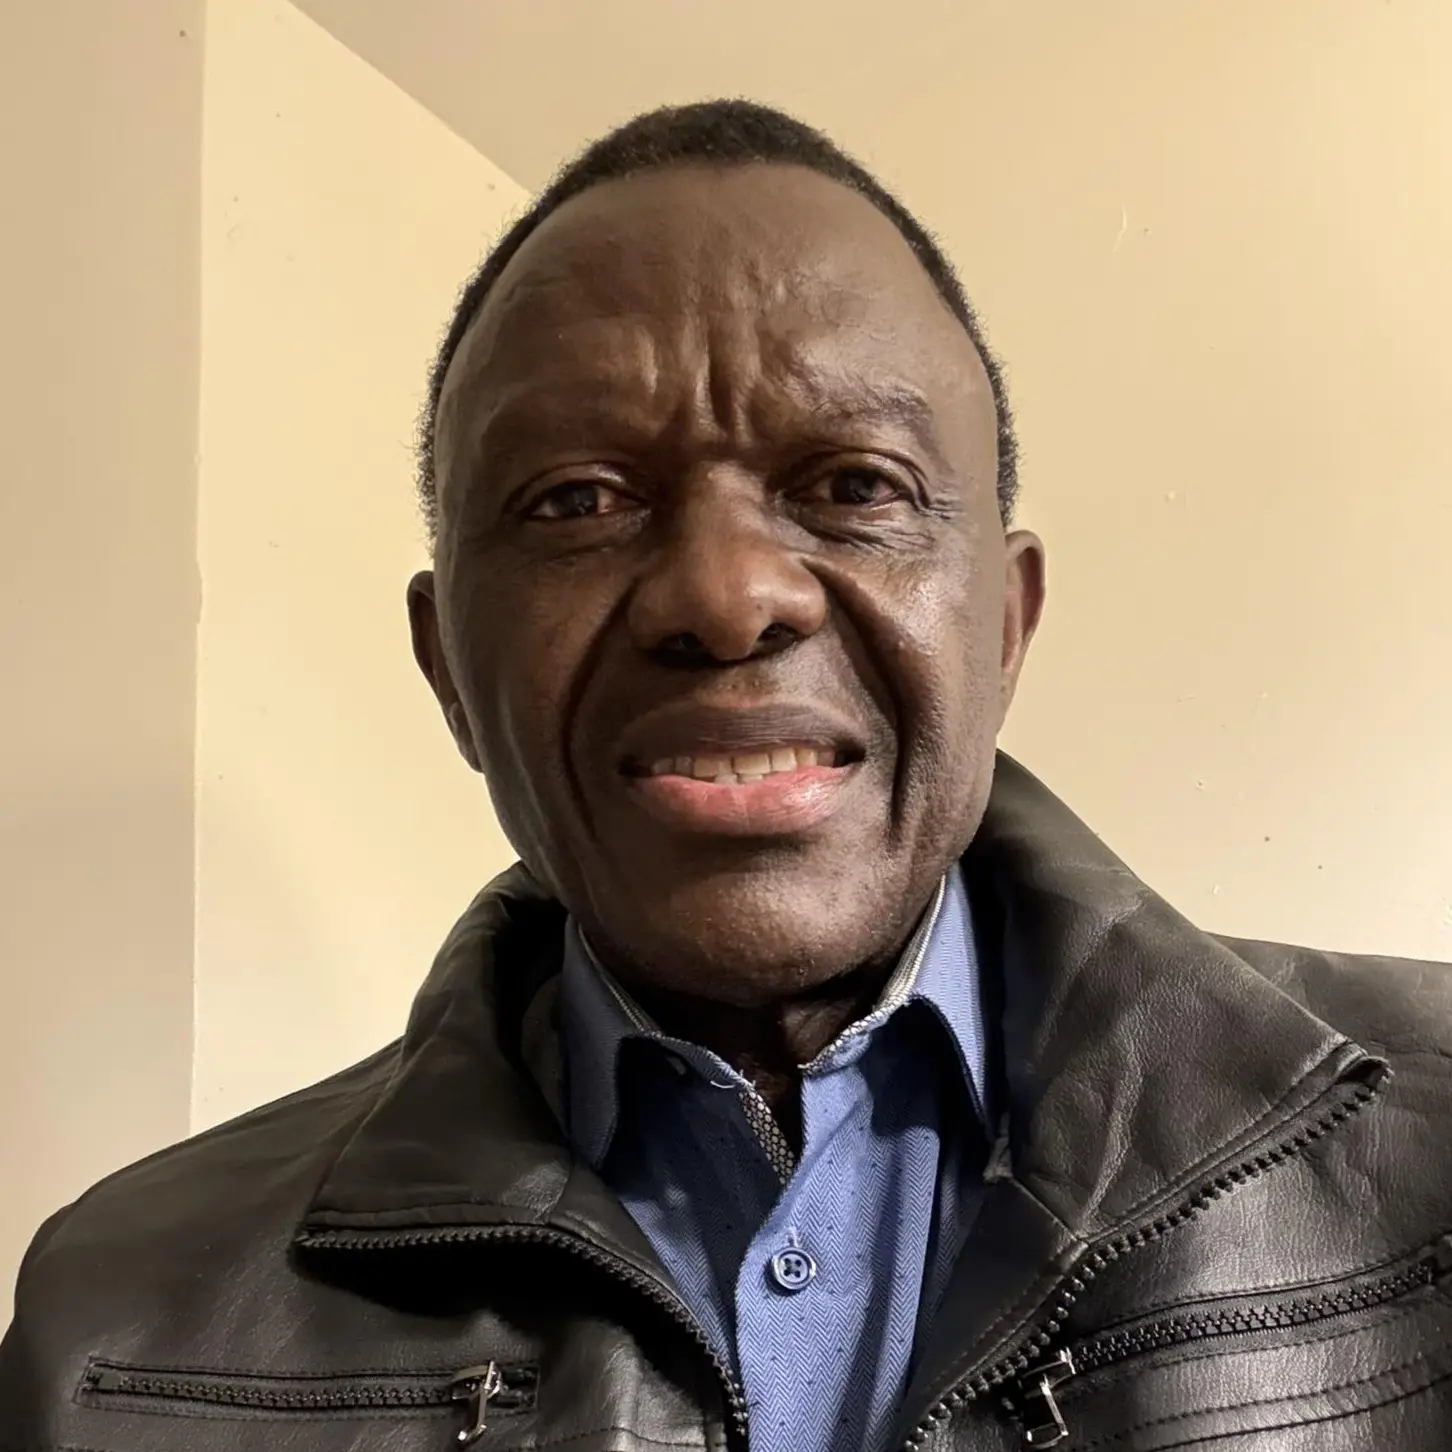
AzanixConsulting.webp
images.assets-landingi.com/uc/8e8e59b4-d2dd-422a-bafc-922cd7251511/ |
97 KB 98 KB |
479ms
396ms |
Image
image/webp |
172.67.73.53 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
jquery-3-6-0.min.js
Show response
assetslp.link/assets/js/landend/ |
87 KB 31 KB |
96ms
24ms |
Script
text/javascript |
99.84.160.9 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
css
fonts.googleapis.com/ |
12 KB 1 KB |
158ms
44ms |
Stylesheet
text/css |
142.251.167.95 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
css
fonts.googleapis.com/ |
33 KB 2 KB |
157ms
45ms |
Stylesheet
text/css |
142.251.167.95 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
css
fonts.googleapis.com/ |
35 KB 2 KB |
154ms
43ms |
Stylesheet
text/css |
142.251.167.95 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
170325-landend-base.css
styles.assets-landingi.com/assets/css/ |
78 KB 17 KB |
93ms
31ms |
Stylesheet
text/css |
172.67.73.53 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
base.css
styles.assets-landingi.com/G0GcIV6eaC7EkOAs/ |
92 KB 12 KB |
476ms
415ms |
Stylesheet
text/css |
172.67.73.53 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
install-code
Show response
popups.landingi.com/api/v3/landing/ |
0 264 B |
329ms
258ms |
Script
text/javascript |
13.33.252.127 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
lightbox-render.js
Show response
scripts.assets-landingi.com/landend/190825/ |
18 KB 6 KB |
408ms
405ms |
Script
text/javascript |
172.67.73.53 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
icon_7efece7ff396c3f4d0ca56246a67dfa4ca46e086.svg
icons.assets-landingi.com/ |
437 B 748 B |
120ms
30ms |
Image
image/svg+xml |
13.32.241.17 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
icon_cdb70c2925205b76967233dd591fad125d40a6ba.svg
icons.assets-landingi.com/ |
532 B 856 B |
118ms
28ms |
Image
image/svg+xml |
13.32.241.17 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
icon_da14c66db335f37fded0f6cf3f7350626b8293d6.svg
icons.assets-landingi.com/ |
1 KB 1 KB |
30ms
26ms |
Image
image/svg+xml |
13.32.241.17 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
icon_f9a3b8ce4042f2fccc9a8ecc062dc08acc1d620d.svg
icons.assets-landingi.com/ |
691 B 1015 B |
44ms
39ms |
Image
image/svg+xml |
13.32.241.17 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
files.js
Show response
scripts.assets-landingi.com/landend/160721/ |
784 B 872 B |
33ms
32ms |
Script
application/javascript |
172.67.73.53 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
jquery.form.min.js
Show response
old.assets-landingi.com/assets/js/vendor/jquery-form/ |
17 KB 7 KB |
45ms
38ms |
Script
application/javascript |
172.67.73.53 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
new_landend.js
Show response
scripts.assets-landingi.com/landend/141025/ |
12 KB 5 KB |
54ms
37ms |
Script
text/javascript |
172.67.73.53 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
font-awesome.min.css
maxcdn.bootstrapcdn.com/font-awesome/4.3.0/css/ |
23 KB 6 KB |
48ms
25ms |
Stylesheet
text/css |
104.18.11.207 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
e85f4114-1c1d-47b1-ac95-1ae947967c28
Show response
tagmanager.landingi.io/account/ |
5 KB 2 KB |
91ms
20ms |
Fetch
application/json |
3.171.117.19 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
4iCs6KVjbNBYlgoKfw72.woff2
fonts.gstatic.com/s/ubuntu/v21/ |
34 KB 34 KB |
86ms
28ms |
Font
font/woff2 |
172.253.62.94 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
icon_fad7c5cc9a64afff8009dde9818000c253a248ea.svg
icons.assets-landingi.com/ |
350 B 660 B |
25ms
24ms |
Image
image/svg+xml |
13.32.241.17 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
4iCv6KVjbNBYlgoC1CzjsGyN.woff2
fonts.gstatic.com/s/ubuntu/v21/ |
38 KB 38 KB |
127ms
69ms |
Font
font/woff2 |
172.253.62.94 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
memvYaGs126MiZpBA-UvWbX2vVnXBbObj2OVTS-muw.woff2
fonts.gstatic.com/s/opensans/v44/ |
47 KB 47 KB |
99ms
40ms |
Font
font/woff2 |
172.253.62.94 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
4iCv6KVjbNBYlgoCxCvjsGyN.woff2
fonts.gstatic.com/s/ubuntu/v21/ |
29 KB 29 KB |
86ms
31ms |
Font
font/woff2 |
172.253.62.94 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
2000802
Show response
stats.landingi.com/visit/ |
14 B 303 B |
350ms
293ms |
Fetch
application/json |
3.168.102.124 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
render
Show response
lightboxes.landingi.com/api/v1/ |
6 KB 6 KB |
592ms
526ms |
XHR
application/json |
52.85.61.87 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
padlock.png
s3.eu-west-1.amazonaws.com/landingi-editor-uploads/gphMioqWi7KowHEs/ |
4 KB 5 KB |
328ms
120ms |
Other
image/png |
3.5.69.57 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
lightbox_2026_01_30_02_45_59.css
styles.assets-landingi.com/hFmTR49m2ZLbLKKf/ |
25 KB 3 KB |
395ms
394ms |
Stylesheet
text/css |
172.67.73.53 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
css
fonts.googleapis.com/ |
4 KB 642 B |
42ms
41ms |
Stylesheet
text/css |
142.251.167.95 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
icon_eec5fbbbf674a8546031ab2fe7c4db8c59e69830.svg
icons.assets-landingi.com/ |
1019 B 870 B |
22ms
22ms |
Image
image/svg+xml |
13.32.241.17 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
api.js
Show response
www.google.com/recaptcha/ |
2 KB 1 KB |
81ms
51ms |
Script
text/javascript |
142.251.152.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
recaptcha__en.js
Show response
www.gstatic.com/recaptcha/releases/BnqMGSY_YP4cCmbNINHpJPkd/ |
825 KB 347 KB |
72ms
20ms |
Script
text/javascript |
142.250.217.3 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
anchor
Show response
www.google.com/recaptcha/api2/ Frame 0433 |
53 KB 28 KB |
109ms
80ms |
Document
text/html |
142.251.154.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
styles__ltr.css
www.gstatic.com/recaptcha/releases/BnqMGSY_YP4cCmbNINHpJPkd/ Frame 0433 |
81 KB 41 KB |
15ms
14ms |
Stylesheet
text/css |
142.251.154.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
recaptcha__en.js
Show response
www.gstatic.com/recaptcha/releases/BnqMGSY_YP4cCmbNINHpJPkd/ Frame 0433 |
825 KB 0 |
1ms
1ms |
Script
text/javascript |
142.250.217.3 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
webworker.js
www.google.com/recaptcha/api2/ Frame 0433 |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
logo_48.png
www.gstatic.com/recaptcha/api2/ Frame 0433 |
2 KB 2 KB |
14ms
13ms |
Image
image/png |
142.251.154.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
KFO7CnqEu92Fr1ME7kSn66aGLdTylUAMa3yUBA.woff2
fonts.gstatic.com/s/roboto/v48/ Frame 0433 |
39 KB 39 KB |
67ms
31ms |
Font
font/woff2 |
172.253.62.94 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||






Failed requests
These URLs were requested, but there was no response received. You will also see them in the list above.
- Domain
- www.google.com
- URL
- https://www.google.com/recaptcha/api2/webworker.js?hl=en&v=BnqMGSY_YP4cCmbNINHpJPkd
Verdicts & Comments Add Verdict or Comment
48 JavaScript Window variables
Go Pro
Only in urlscan Pro
Inspect and pivot on JavaScript variables, identifiers, and other key site metadata data with urlscan Pro. Reveal and search on client-side frameworks, runtime variables, and custom values.
Click for more information
Free trials of urlscan Pro are available.
These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.
object| 0 object| 1 object| Blinkloader object| landingiInternalDetails object| lazySizesConfig object| lazySizes function| $ function| jQuery object| frodo function| VideoBg function| saveUrlLeadIdToFormInput function| checkUrlForActionAfterSubmission object| validateCallbacks function| registerValidateCallback function| createCookieForCreatio function| addParamsToUrl function| removeParamFromUrl function| getCookie function| getUrlVars function| Cookies function| positionValidationTooltips function| scrollToFirstTooltip function| initRecaptchaOnFormSubmit function| initRecaptchaOnEvent function| waitForJQuery function| recaptchaOnload object| grecaptcha function| initializeNewCounter function| showRemaining function| calculateWidgetValue function| buildEndDate function| isLocalStorageAvailable function| getEndDateFromCookies function| getEndDateFromLocalStorage function| localStorageIsExpired function| saveEndDate function| getParsedAttribute object| youtubeVideos object| youtubePlayers function| onYouTubeIframeAPIReady boolean| isRecaptchaInitialized boolean| isRecaptchaScriptInjected object| ___grecaptcha_cfg string| __recaptcha_api boolean| __google_recaptcha_client object| recaptcha object| closure_lm_674093 function| scrypt1 Cookies
Go Pro
Only in urlscan Pro
Review, search, and pivot on browser cookies and persistence site data to see how a site tracks users and keeps sessions alive across visits.
Click for more information
Free trials of urlscan Pro are available.
Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.
| Domain/Path | Expires | Name / Value | |||
|---|---|---|---|---|---|
| www.contactazanix.com/ | 1970-01-21 17:01:17 |
Name: ls_sid_2000802 Value: 01a09924-21ce-71c6-8361-3f0c44116bd2 |
Security Headers
This page lists any security headers set by the main page. If you want to understand what these mean and how to use them, head on over to this page
| Header | Value |
|---|---|
| Strict-Transport-Security | max-age=7776000; includeSubdomains; preload |
| X-Content-Type-Options | nosniff |
| X-Frame-Options | deny |
Indicators
This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.
assetslp.link
cdn.lugc.link
fonts.googleapis.com
fonts.gstatic.com
icons.assets-landingi.com
images.assets-landingi.com
lightboxes.landingi.com
maxcdn.bootstrapcdn.com
old.assets-landingi.com
popups.landingi.com
s3.eu-west-1.amazonaws.com
scripts.assets-landingi.com
stats.landingi.com
styles.assets-landingi.com
tagmanager.landingi.io
ucarecdn.com
www.contactazanix.com
www.google.com
www.gstatic.com
www.google.com
104.18.11.207
13.32.241.17
13.33.252.127
142.250.217.3
142.251.152.119
142.251.154.119
142.251.167.95
151.101.193.55
151.101.2.132
157.53.227.1
172.253.62.94
172.67.73.53
3.168.102.124
3.171.117.19
3.5.69.57
52.85.61.87
99.84.160.9
161d27ca0cc34eadcf24f062b98fda9c8a6a35f1e7d184218a80942f36470e39
1930640faa7d5082f7bcbd33b73b1701f17231085a7254b1749412bd8d28bfb8
1b9efb22c938500971aac2b2130a475fa23684dd69e43103894968df83145b8a
1d621601dc5d76c78a9b7d9e7a92f807d575e90b87b3694db478d791b78ca9c3
20b535fa80c8189e3b87d1803038389960203a886d502bc2ef1857affc2f38d2
3658a0717e347c1db8d80dd565584b9dc56769fbf87909c50a4a7740206ec5f7
3b391fb598965dc19525604e05327756d6b2bc5b4f221f5f76d1537474e4d936
46bad547480f9d36f1fae5c9e78baa33c70341dbe827afca68a5202c2cb2f7f3
46ef20c3bf16f3011c2c15cfd31558eedc534b0969264691d6ab0ca887f5303f
4d3682f339141860b1a188bbc2bb2f055d9506fcde5d24d84a8a29dea5ca2c2e
4d8c5aaf43bf8d6650515ec9351a62fdfca87b46462e1c2c880af0212c8c6ffc
53559107fc962d3fa47002484b1d39707ea5e1d15d69cb91072481e0cb098491
541ac58217a8ade1a5e292a65a0661dc9db7a49ae13654943817a4fbc6761afd
568e99dcc13a15dc789bc1696bb284cb04396bd1d25c2c3e7e0eb40994e2f037
5febeac85565bfc5faa121512cbb10e563f25a4ecd36917a0ad368fce9b4b668
629caca5de3359a82a966a616c98ada8832dac4c5f57df2a16ee024767714921
65b09a5d8fd48badeb70068deed8d5449865c8328cc77521828bc270e28dc3a3
667ac5e4db495c2d710d693580bfe9b40e6084a82f943b22b4446e428578eb75
6722074dff8a51080df57424c32129ae34699a4bde93e5adb319977dc52840a4
69c838400faebb1fb231ec57d630c735918c0f080879af9ef4d6f3c37acfff80
83629765c5f8ece4d67ea8f1a12ada27f1988286718be113697786ef19193e63
863908242752e100c6699183b5b7f51815c4fd838d776d13434b3613a3029694
8dab2ed9335b89835d238038e3bb74ca781ba12de569096b8fedf284cff763d8
910c936e23b0368dda2386aeb2296cf070575610a556efe4d6144c4d98246a02
951342e8bdeca44307804d3e0a9d96cb59759e51312fa375c7ea645ffa1c487c
9951b58b76a51c9236163a991ef81d2d3a1239e9918c65466d05eeaafbc35fd8
998fb9fd2f2845f623afa3fad936a4c832f7213cbb153450ff2908088ca418b4
9b6a1e051b81f9b4e5b77b5d045a743f1e6e1607f457b4076fc4d6c52f5b3a72
aa590832f4fa4778fa3442dafb2752a26147966f85a4b2f58262a22d92e2c398
b15c41dc4f6a786cc2e35b9e370112b1663aaa124b3ead576b7d23cd4399d7f0
b259dd4d8653ea89a7ac09ab6650fac0f6dcb13a2766cd63d7ef0b2c02fcb5f9
b877399df84b57fc23f2aab1654bc0616f7ce4a0cdd7c5042c5c586d49d6a60f
c65846dc04fe1ab20f608c728a993ac69e583cb4880f45815b8c2ef436550b2a
d0caddaff8519db49e8ad6a49b8089490fdb910fab6bf31212d59eae72f60132
d1dabf93704f2094911c86769899acb8c0c87be646a58841a6b8f7695e0b50ef
d8e4fe0452aa2076429a9bb5d8757d00a994dd95986cf950e9a1a371b9a072a0
d8f8ebd4e96964c63aa9eb0933af2ddafdfdb7e94c2efc70a5af109518c9ae80
dabae363ac0ae6c3b2a137a32f7132b42520a8af252f87aa6c2198f2a79cf91c
e0c74eac86a19d782c3ec35ff3b1ff13b5882bf7176fc5a61b41b0b3633b945d
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
ebd87d773f831bcda3c0b80d032490c3ddf2995953bfdae3225f144000d4186f
fdb09c0fad1cea442dd09a42a2f8173df4890d14da23566e2c92c57e80ef5aa0
ff1523fb7389539c84c65aba19260648793bb4f5e29329d2ee8804bc37a3fe6e