
proma.global
104.21.8.240
Public Scan
Open in
urlscan Pro
http://promaoptimumhealth.com.au/ 10yr old
Effective URL:
https://proma.global/optimum-health 7yr old
Submission: On September 13 via api (September 13th 2026, 3:42:35 pm UTC) from US — Scanned from AU Go Pro
Only in urlscan Pro
- Select different country locations for Private Scans.
- Use a global network of additional scanning locations and residential IPs for scanning.
- Interact with pages while you are scanning them.
- Download files from remote websites.
- Scan websites on the Tor Network.
Summary
TLS certificate: Issued by WE1 on August 14th 2026. Valid for: 3mo.
This is the only time proma.global was scanned on urlscan.io!
urlscan.io Verdict: No classification
Domain & IP information
| IP Address | AS Autonomous System | ||
|---|---|---|---|
| 1 1 | 172.67.202.234 172.67.202.234 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 14 | 104.21.8.240 104.21.8.240 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 5 | 184.84.165.106 184.84.165.106 | 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.) | |
| 7 | 172.64.147.188 172.64.147.188 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 151.101.1.155 151.101.1.155 | 54113 (FASTLY) (FASTLY - Fastly) | |
| 2 | 104.17.208.5 104.17.208.5 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 3 | 104.17.25.14 104.17.25.14 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 33 | 2.18.224.45 2.18.224.45 | 16625 (AKAMAI-AS) (AKAMAI-AS - Akamai Technologies) | |
| 1 | 104.16.79.73 104.16.79.73 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 23.46.179.155 23.46.179.155 | 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.) | |
| 3 | 142.251.42.104 142.251.42.104 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 2 | 35.190.88.7 35.190.88.7 | 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC) | |
| 2 | 157.240.8.23 157.240.8.23 | 32934 (FACEBOOK) (FACEBOOK - Facebook) | |
| 4 | 142.251.157.119 142.251.157.119 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 142.250.195.134 142.250.195.134 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 54.177.251.2 54.177.251.2 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 1 | 157.240.8.35 157.240.8.35 | 32934 (FACEBOOK) (FACEBOOK - Facebook) | |
| 1 | 216.239.34.181 216.239.34.181 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 74.125.200.157 74.125.200.157 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 2 | 172.217.25.163 172.217.25.163 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 142.250.195.130 142.250.195.130 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 86 | 21 |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| promaoptimumhealth.com.au 10yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| proma.global 7yr old |
ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL)
PTR: a184-84-165-106.deploy.static.akamaitechnologies.com
| use.typekit.net 14yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| kit.fontawesome.com 7yr old | |
| ka-p.fontawesome.com 7yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| cdn.jsdelivr.net 14yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| cdnjs.cloudflare.com 13yr old |
ASN16625 (AKAMAI-AS - Akamai Technologies, Inc., US)
PTR: a2-18-224-45.deploy.static.akamaitechnologies.com
| res.cloudinary.com 10yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| static.cloudflareinsights.com 7yr old |
ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL)
PTR: a23-46-179-155.deploy.static.akamaitechnologies.com
| p.typekit.net 14yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: bom07s45-in-f8.1e100.net
| www.googletagmanager.com 14yr old |
ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US)
PTR: 7.88.190.35.bc.googleusercontent.com
| sessions.bugsnag.com 9yr old |
ASN32934 (FACEBOOK - Facebook, Inc., US)
PTR: xx-fbcdn-shv-01-syd2.fbcdn.net
| connect.facebook.net 14yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: maa03s40-in-f6.1e100.net
| ad.doubleclick.net 10yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: ec2-54-177-251-2.us-west-1.compute.amazonaws.com
| k6-e4e4123be8e54363900a90353991ca93.ecs.us-west-1.on.aws 7mo old |
ASN32934 (FACEBOOK - Facebook, Inc., US)
PTR: edge-star-mini-shv-01-syd2.facebook.com
| www.facebook.com 11yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: sa-in-f157.1e100.net
| stats.g.doubleclick.net 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: pnsyda-ai-in-f3.1e100.net
| www.google.com.au 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: tzsyda-ab-in-f2.1e100.net
| googleads.g.doubleclick.net 10yr old |
| Apex Domain Subdomains |
Transfer | |
|---|---|---|
| 33 |
cloudinary.com
res.cloudinary.com — Cisco Umbrella Rank: 3954 10yr old |
3 MB |
| 14 |
proma.global
1 redirects
proma.global 7yr old |
248 KB |
| 7 |
fontawesome.com
kit.fontawesome.com — Cisco Umbrella Rank: 2490 7yr old ka-p.fontawesome.com — Cisco Umbrella Rank: 3690 7yr old |
33 KB |
| 6 |
typekit.net
use.typekit.net — Cisco Umbrella Rank: 562 14yr old p.typekit.net — Cisco Umbrella Rank: 687 14yr old |
121 KB |
| 5 |
google.com
www.google.com — Cisco Umbrella Rank: 3 14yr old analytics.google.com — Cisco Umbrella Rank: 143 9yr old |
64 B |
| 3 |
doubleclick.net
ad.doubleclick.net — Cisco Umbrella Rank: 128 10yr old stats.g.doubleclick.net — Cisco Umbrella Rank: 156 10yr old googleads.g.doubleclick.net — Cisco Umbrella Rank: 66 10yr old |
3 KB |
| 3 |
googletagmanager.com
www.googletagmanager.com — Cisco Umbrella Rank: 44 14yr old |
541 KB |
| 3 |
cloudflare.com
cdnjs.cloudflare.com — Cisco Umbrella Rank: 284 13yr old |
12 KB |
| 2 |
google.com.au
www.google.com.au — Cisco Umbrella Rank: 10125 10yr old |
127 B |
| 2 |
facebook.net
connect.facebook.net — Cisco Umbrella Rank: 224 14yr old |
243 KB |
| 2 |
bugsnag.com
sessions.bugsnag.com — Cisco Umbrella Rank: 1159 9yr old |
131 B |
| 2 |
jsdelivr.net
cdn.jsdelivr.net — Cisco Umbrella Rank: 281 14yr old |
53 KB |
| 1 |
facebook.com
www.facebook.com — Cisco Umbrella Rank: 132 11yr old |
20 B |
| 1 |
on.aws
k6-e4e4123be8e54363900a90353991ca93.ecs.us-west-1.on.aws — Cisco Umbrella Rank: 9495 7mo old |
|
| 1 |
cloudflareinsights.com
static.cloudflareinsights.com — Cisco Umbrella Rank: 307 7yr old |
10 KB |
| 1 |
jquery.com
code.jquery.com — Cisco Umbrella Rank: 849 13yr old |
83 KB |
| 1 |
promaoptimumhealth.com.au
1 redirects
promaoptimumhealth.com.au 10yr old |
607 B |
| 0 |
site.com
Failed
proma.my.site.com Failed 2yr old |
|
| 86 | 18 |
| Domain | Requested by | |
|---|---|---|
| 33 | res.cloudinary.com |
proma.global
|
| 14 | proma.global |
1 redirects
proma.global
|
| 6 | ka-p.fontawesome.com |
proma.global
|
| 5 | use.typekit.net |
proma.global
use.typekit.net |
| 4 | www.google.com |
proma.global
|
| 3 | www.googletagmanager.com |
proma.global
www.googletagmanager.com |
| 3 | cdnjs.cloudflare.com |
proma.global
|
| 2 | www.google.com.au |
proma.global
|
| 2 | connect.facebook.net |
proma.global
connect.facebook.net |
| 2 | sessions.bugsnag.com |
proma.global
|
| 2 | cdn.jsdelivr.net |
proma.global
|
| 1 | googleads.g.doubleclick.net |
www.googletagmanager.com
|
| 1 | stats.g.doubleclick.net |
www.googletagmanager.com
|
| 1 | analytics.google.com |
proma.global
|
| 1 | www.facebook.com |
proma.global
|
| 1 | k6-e4e4123be8e54363900a90353991ca93.ecs.us-west-1.on.aws |
proma.global
|
| 1 | ad.doubleclick.net |
proma.global
|
| 1 | p.typekit.net |
use.typekit.net
|
| 1 | static.cloudflareinsights.com |
proma.global
|
| 1 | code.jquery.com |
proma.global
|
| 1 | kit.fontawesome.com |
proma.global
|
| 1 | promaoptimumhealth.com.au | 1 redirects |
| 0 | proma.my.site.com Failed |
proma.global
|
| 86 | 23 |
This site contains links to these domains. Also see Links.
| Domain |
|---|
| www.facebook.com |
| directselling.org.au |
| policies.google.com |
| Subject Issuer | Validity | Valid | |
|---|---|---|---|
| proma.global WE1 |
2026-08-14 - 2026-11-12 |
3mo | crt.sh |
| use.typekit.net DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2026-05-29 - 2026-12-13 |
7mo | crt.sh |
| fontawesome.com WE1 |
2026-08-12 - 2026-11-10 |
3mo | crt.sh |
| *.jquery.com Sectigo Public Server Authentication CA DV E36 |
2026-05-20 - 2026-12-04 |
7mo | crt.sh |
| *.jsdelivr.net Sectigo Public Server Authentication CA DV R36 |
2026-04-22 - 2026-11-06 |
7mo | crt.sh |
| cdnjs.cloudflare.com WE1 |
2026-09-07 - 2026-12-06 |
3mo | crt.sh |
| *.cloudinary.com Go Daddy Secure Certificate Authority - G2 |
2026-01-11 - 2027-02-10 |
1yr | crt.sh |
| cloudflareinsights.com WE1 |
2026-08-14 - 2026-11-12 |
3mo | crt.sh |
| *.google-analytics.com WR2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| *.bugsnag.com DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2026-03-27 - 2026-10-11 |
7mo | crt.sh |
| *.facebook.com DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2026-06-22 - 2026-09-20 |
3mo | crt.sh |
| *.google.com WR2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| *.doubleclick.net WR2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| k6-e4e4123be8e54363900a90353991ca93.ecs.us-west-1.on.aws Amazon ECDSA 256 M01 |
2026-06-10 - 2026-12-24 |
7mo | crt.sh |
| *.g.doubleclick.net WR2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
| *.google.com.au WR2 |
2026-08-10 - 2026-11-02 |
3mo | crt.sh |
This page contains 3 frames:
Primary Page:
https://proma.global/optimum-health
Frame ID: 9C669E89E79B2348C7939E2025356436
Requests: 85 HTTP requests in this frame
Frame:
https://proma.global/cdn-cgi/challenge-platform/h/g/scripts/jsd/330e41bb475c/main.js
Frame ID: 44D10E27FAEC519A16132AC6339EDDE5
Requests: 2 HTTP requests in this frame
Frame:
https://www.facebook.com/tr/
Frame ID: A8328E8CCE7801E6CBFC5BB773B8FC03
Requests: 1 HTTP requests in this frame
Screenshot
Go Pro
Only in urlscan Pro
Use the Visual Search feature to find pages with visually similar screenshots.
Click for more information
Free trials of urlscan Pro are available.
Page Title
Optimum HealthPage URL History
Go Pro
Only in urlscan Pro
Search our real-time database of newly observed domains and
hostnames. Pivot on different attributes, and setup keyword alerts for
newly observed domains.
Click for more information
Free trials of urlscan Pro are available.
Show full URLs
-
http://promaoptimumhealth.com.au/
HTTP 307
https://promaoptimumhealth.com.au/ HTTP 301
https://proma.global/optimum-health Page URL
Detected technologies
 Bootstrap
(UI frameworks)
Expand
Detected patterns
- (?:/|-)bootstrap(?:[^/]*?([0-9a-fA-F]{7,40}|[\d]+(?:\.[\d]+(?:\.[\d]+)?)?)|)[^/]*?(?:\.min)?\.js
 cdnjs
(CDN)
Expand
Detected patterns
- cdnjs\.cloudflare\.com
 Cloudflare Browser Insights
(Analytics)
Expand
Detected patterns
- static\.cloudflareinsights\.com/beacon(?:\.min)?\.js
 DoubleClick Floodlight
(Advertising)
Expand
Detected patterns
- \.doubleclick\.net
 Facebook Pixel
(Analytics)
Expand
Detected patterns
- connect\.facebook\.\w+/.+/fbevents\.js
- connect\.facebook.\w+/signals/config/\d+\?v=([\d\.]+)
 Font Awesome
(Font scripts)
Expand
Detected patterns
- (?:F|f)o(?:n|r)t-?(?:A|a)wesome(?:.*?([0-9a-fA-F]{7,40}|[\d]+(?:.[\d]+(?:.[\d]+)?)?)|)
- \.fontawesome\.com/([0-9a-z]+).js
 Google Analytics
(Analytics)
Expand
Detected patterns
- googletagmanager\.com/gtag/js
 Google Tag Manager
(Tag managers)
Expand
Detected patterns
- googletagmanager\.com/gtm\.js
- \.googletagmanager\.com/
 jQuery
(JavaScript libraries)
Expand
Detected patterns
- jquery
- /jquery(?:-(\d+\.\d+\.\d+))[/.-]
jQuery CDN
(CDN)
Expand
Detected patterns
- code\.jquery\.com/
 jsDelivr
(CDN)
Expand
Detected patterns
- cdn\.jsdelivr\.net
 Slick
(JavaScript libraries)
Expand
Detected patterns
- (?:/([\d.]+))?/slick(?:\.min)?\.js
Page Statistics
4 Outgoing links
Go Pro
Only in urlscan Pro
Effortlessly use any on-page link as a pivot to discover other pages pointing to the exact same destination. Seamlessly trace both specific URLs and broader domains to uncover hidden connection networks and map out backlink relationships with ease.
Click for more information
Free trials of urlscan Pro are available.
These are links going to different origins than the main page.
Search URL Search Domain Scan URL
Title: Code of Practice.
Search URL Search Domain Scan URL
Title: Privacy Policy
Search URL Search Domain Scan URL
Title: Terms of Service
Search URL Search Domain Scan URL
Page URL History
This captures the URL locations of the websites, including HTTP redirects and client-side redirects via JavaScript or Meta fields.
-
http://promaoptimumhealth.com.au/
HTTP 307
https://promaoptimumhealth.com.au/ HTTP 301
https://proma.global/optimum-health Page URL
Redirected requests
There were HTTP redirect chains for the following requests:
Request Chain 66- https://proma.global/cdn-cgi/challenge-platform/scripts/jsd/main.js HTTP 302
- https://proma.global/cdn-cgi/challenge-platform/h/g/scripts/jsd/330e41bb475c/main.js
86 HTTP transactions
Go Pro
Only in urlscan Pro
Inspect WebSocket connections, examine POST data effortlessly, and track overlap counts in real time. Features live search and filtering across all HTTP output, complete with full response metadata for deep analysis.
Click for more information
Free trials of urlscan Pro are available.
3 data transactions
| Method Protocol |
Status | Resource Path |
Size x-fer |
Time Latency |
Type MIME-Type |
IP Location |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
|
GET H3 |
200 |
Primary Request
optimum-health
Show response
proma.global/ Redirect Chain
|
740 KB 161 KB |
2099ms
2066ms |
Document
text/html |
104.21.8.240 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
theme.CUBHHUIC.css
proma.global/assets/styles/ |
267 KB 30 KB |
41ms
40ms |
Stylesheet
text/css |
104.21.8.240 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
configure.U43DPAZA.js
Show response
proma.global/assets/scripts/ |
109 KB 32 KB |
41ms
37ms |
Script
text/javascript |
104.21.8.240 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
metadata.SPFREYAW.js
Show response
proma.global/assets/scripts/ |
1 KB 2 KB |
36ms
32ms |
Script
text/javascript |
104.21.8.240 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
theme.5HZGC4UI.js
Show response
proma.global/assets/scripts/ |
7 KB 3 KB |
47ms
43ms |
Script
text/javascript |
104.21.8.240 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
xie8ewv.css
use.typekit.net/ |
7 KB 1 KB |
1009ms
899ms |
Stylesheet
text/css |
184.84.165.106 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
7d3f741cb3.js
Show response
kit.fontawesome.com/ |
16 KB 6 KB |
339ms
267ms |
Script
text/javascript |
172.64.147.188 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
jquery-3.6.0.js
Show response
code.jquery.com/ |
282 KB 83 KB |
92ms
21ms |
Script
application/javascript |
151.101.1.155 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
bootstrap.min.css
cdn.jsdelivr.net/npm/bootstrap@5.2.3/dist/css/ |
190 KB 29 KB |
95ms
23ms |
Stylesheet
text/css |
104.17.208.5 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
bootstrap.bundle.min.js
Show response
cdn.jsdelivr.net/npm/bootstrap@5.2.3/dist/js/ |
79 KB 24 KB |
25ms
24ms |
Script
application/javascript |
104.17.208.5 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
slick.min.css
cdnjs.cloudflare.com/ajax/libs/slick-carousel/1.8.1/ |
1 KB 1001 B |
67ms
43ms |
Stylesheet
text/css |
104.17.25.14 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
slick-theme.min.css
cdnjs.cloudflare.com/ajax/libs/slick-carousel/1.8.1/ |
2 KB 1 KB |
55ms
31ms |
Stylesheet
text/css |
104.17.25.14 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
slick.min.js
Show response
cdnjs.cloudflare.com/ajax/libs/slick-carousel/1.8.1/ |
42 KB 10 KB |
54ms
30ms |
Script
application/javascript |
104.17.25.14 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
menu.F3K6AAAQ.js
Show response
proma.global/assets/scripts/ |
5 KB 3 KB |
45ms
43ms |
Script
text/javascript |
104.21.8.240 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
proma-systems-svg-web-logo.svg
res.cloudinary.com/hpf2bgvwe/image/upload/v1753772868/media/00d2v000003qbb7eao/ |
4 KB 2 KB |
182ms
68ms |
Image
image/svg+xml |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
404 |
icon-times-a9d9b3d3b9fa891bc2954d51cfef7800c60033eb784d0f952e2be73642f996d4.png
proma.global/assets/icons/ |
14 B 14 B |
40ms
39ms |
Image
text/plain |
104.21.8.240 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
flash.3VUNNVGM.js
Show response
proma.global/assets/scripts/ |
361 B 1 KB |
42ms
42ms |
Script
text/javascript |
104.21.8.240 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
quantity-picker.K2KRPY36.js
Show response
proma.global/assets/scripts/ |
4 KB 3 KB |
37ms
36ms |
Script
text/javascript |
104.21.8.240 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
optimum-health-banner-image-v2-cropped.jpg
res.cloudinary.com/hpf2bgvwe/image/upload/v1753777864/media/00d2v000003qbb7eao/ |
240 KB 240 KB |
48ms
47ms |
Image
image/jpeg |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
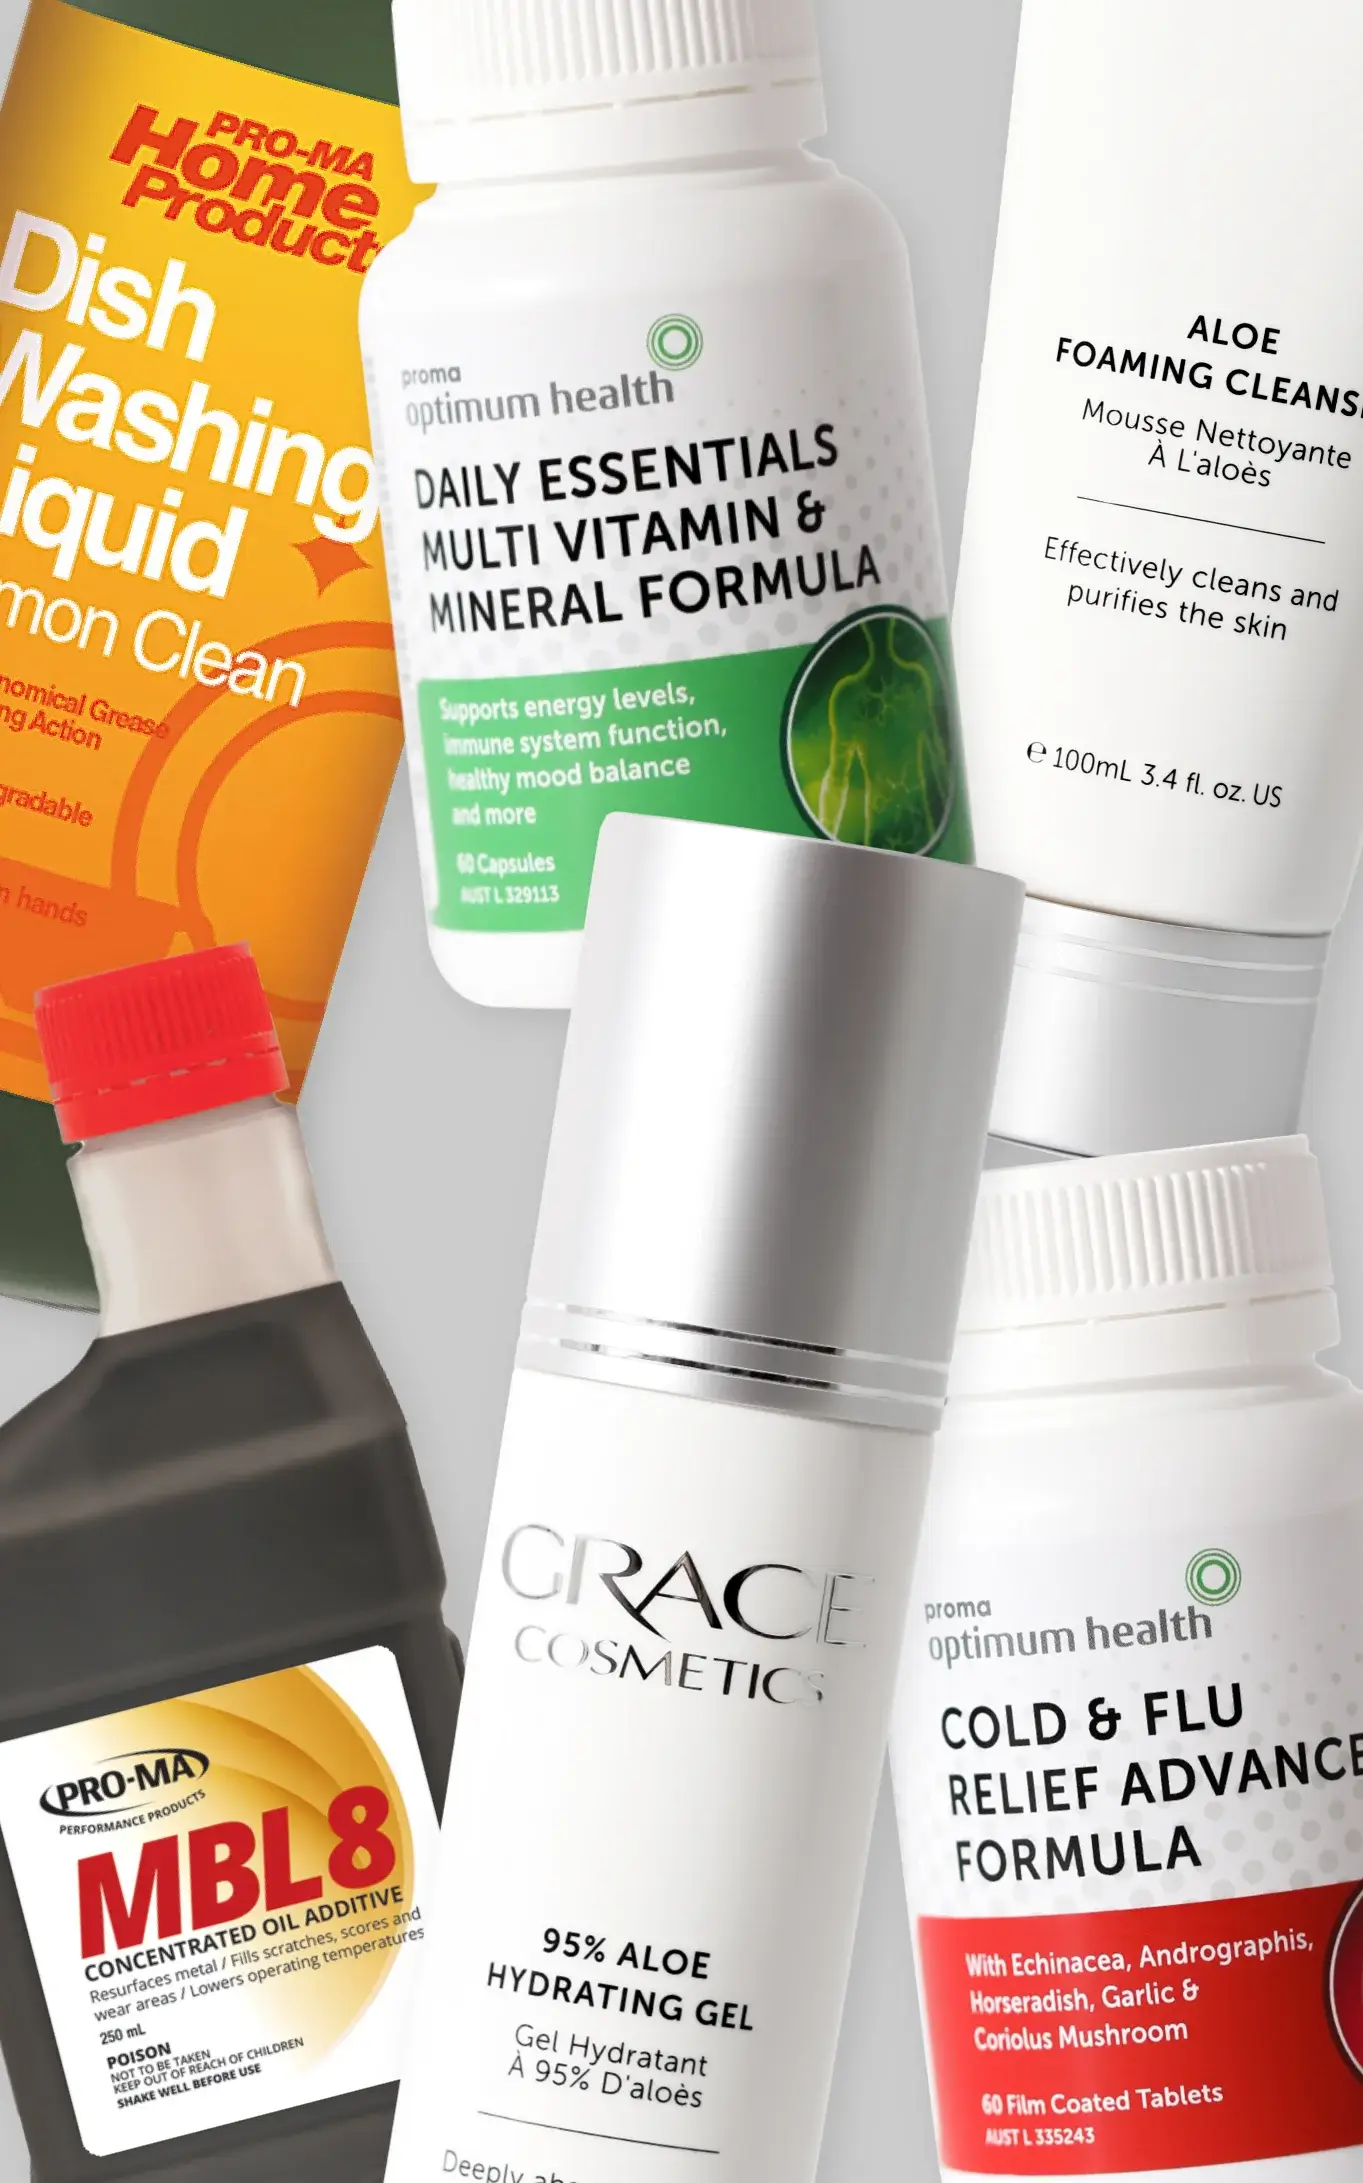
optimum-health-products_assortment.jpg
res.cloudinary.com/hpf2bgvwe/image/upload/v1753773755/media/00d2v000003qbb7eao/ |
176 KB 176 KB |
114ms
114ms |
Image
image/jpeg |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Our_Values_Icons_V2_australian-owned.png
res.cloudinary.com/hpf2bgvwe/image/upload/v1753773737/media/00d2v000003qbb7eao/ |
45 KB 46 KB |
48ms
47ms |
Image
image/png |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Our_Values_Icons_V2_formulas-backed-by-science.png
res.cloudinary.com/hpf2bgvwe/image/upload/v1753773752/media/00d2v000003qbb7eao/ |
36 KB 36 KB |
46ms
45ms |
Image
image/png |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Our_Values_Icons_V2_TGA-approved.png
res.cloudinary.com/hpf2bgvwe/image/upload/v1753773750/media/00d2v000003qbb7eao/ |
30 KB 31 KB |
45ms
45ms |
Image
image/png |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Our_Values_Icons_V2_eco-friendly-biodegradable.png
res.cloudinary.com/hpf2bgvwe/image/upload/v1753773730/media/00d2v000003qbb7eao/ |
45 KB 46 KB |
46ms
46ms |
Image
image/png |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Our_Values_Icons_V2_caring-for-the-enviroment2.webp
res.cloudinary.com/hpf2bgvwe/image/upload/v1753778491/media/00d2v000003qbb7eao/ |
6 KB 6 KB |
49ms
48ms |
Image
image/webp |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
optimum-health-tablets_assortment.jpg
res.cloudinary.com/hpf2bgvwe/image/upload/v1753773757/media/00d2v000003qbb7eao/ |
128 KB 129 KB |
52ms
51ms |
Image
image/jpeg |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
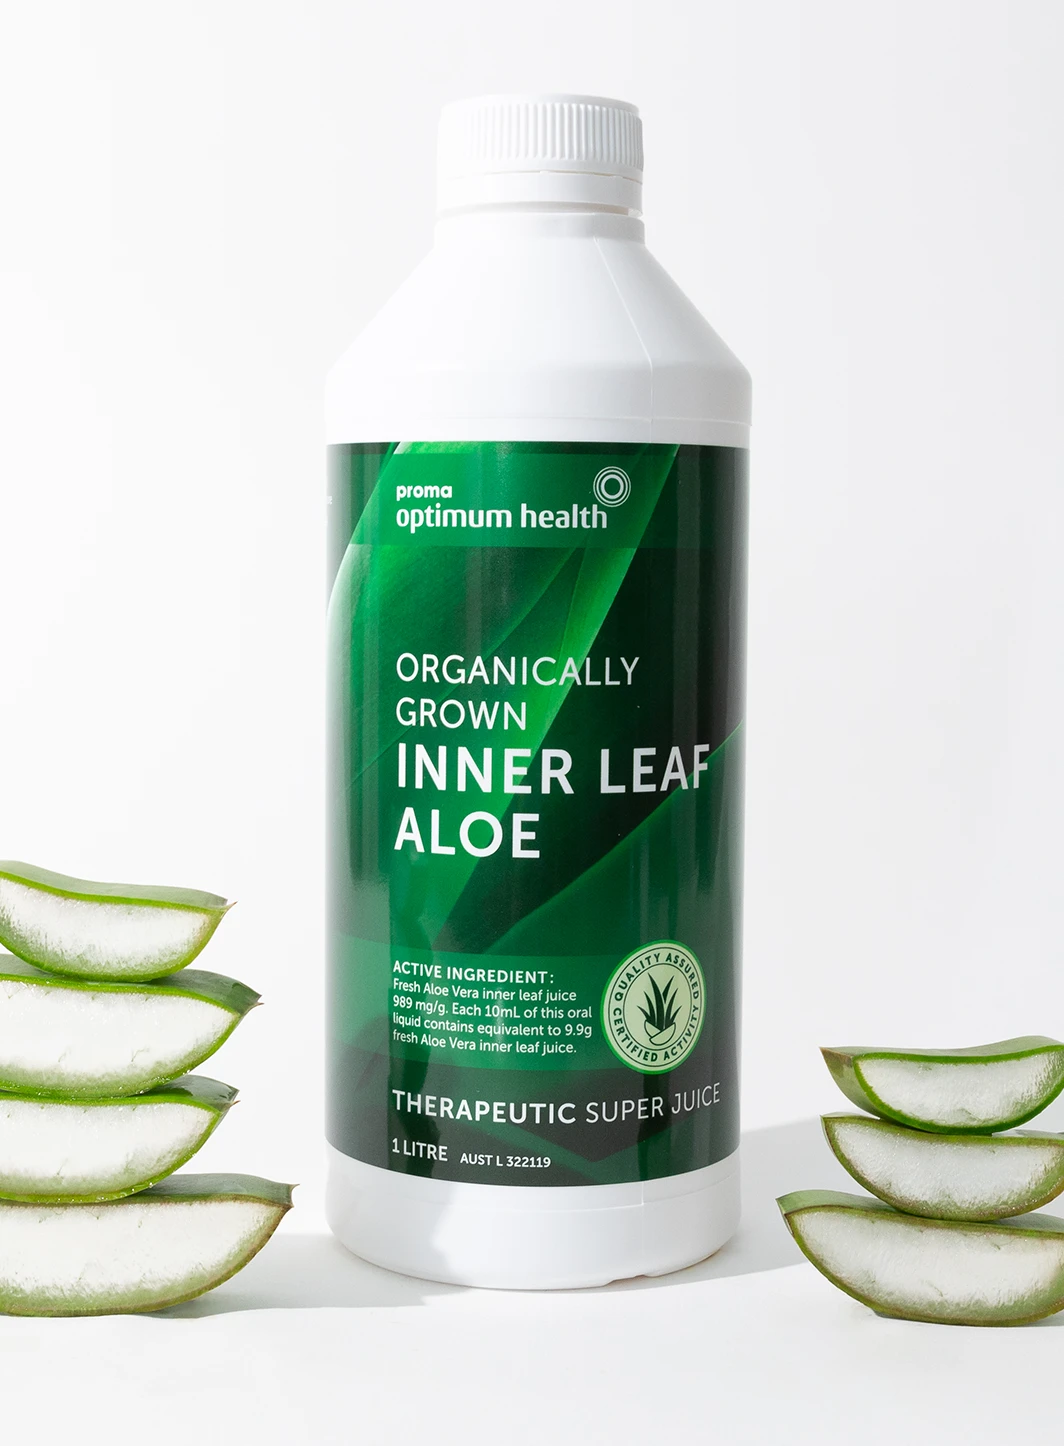
aloe-juice-product_ad2.webp
res.cloudinary.com/hpf2bgvwe/image/upload/v1753778708/media/00d2v000003qbb7eao/ |
217 KB 217 KB |
79ms
79ms |
Image
image/webp |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
facebook-logo-icon.svg
res.cloudinary.com/hpf2bgvwe/image/upload/v1753779093/media/00d2v000003qbb7eao/ |
902 B 1 KB |
53ms
53ms |
Image
image/svg+xml |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
tik-tok-logo-icon.svg
res.cloudinary.com/hpf2bgvwe/image/upload/v1753779098/media/00d2v000003qbb7eao/ |
1 KB 1 KB |
59ms
59ms |
Image
image/svg+xml |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
custom-form-answers.P67VH5YU.js
Show response
proma.global/assets/scripts/ |
4 KB 2 KB |
40ms
39ms |
Script
text/javascript |
104.21.8.240 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
v31edd6df95cf4e85bb4c19e7a9bdbcba1788362987495
Show response
static.cloudflareinsights.com/beacon.min.js/ |
30 KB 10 KB |
91ms
28ms |
Script
text/javascript |
104.16.79.73 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
p.css
p.typekit.net/ |
5 B 172 B |
205ms
103ms |
Stylesheet
text/css |
23.46.179.155 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
pro-v4-shims.min.js
Show response
ka-p.fontawesome.com/releases/v6.7.2/js/ |
27 KB 8 KB |
34ms
26ms |
Fetch
application/javascript |
172.64.147.188 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
pro.min.js
Show response
ka-p.fontawesome.com/releases/v6.7.2/js/ |
54 KB 17 KB |
38ms
31ms |
Fetch
application/javascript |
172.64.147.188 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
gtm.js
Show response
www.googletagmanager.com/ |
502 KB 165 KB |
458ms
204ms |
Script
application/javascript |
142.251.42.104 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
l
use.typekit.net/af/1be3c2/00000000000000007735e606/30/ |
30 KB 30 KB |
212ms
110ms |
Font
application/font-woff2 |
184.84.165.106 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
l
use.typekit.net/af/efe4a5/00000000000000007735e609/30/ |
29 KB 29 KB |
188ms
86ms |
Font
application/font-woff2 |
184.84.165.106 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
l
use.typekit.net/af/2555e1/00000000000000007735e603/30/ |
30 KB 30 KB |
162ms
60ms |
Font
application/font-woff2 |
184.84.165.106 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Proma_Gift_Card_-_Ad_Card-V2.webp
res.cloudinary.com/hpf2bgvwe/image/upload/v1753779298/media/00d2v000003qbb7eao/ |
53 KB 53 KB |
56ms
55ms |
Image
image/webp |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Everyday-Go-To-AdCard-0125.jpg
res.cloudinary.com/hpf2bgvwe/image/upload/v1753779422/media/00d2v000003qbb7eao/ |
127 KB 127 KB |
59ms
58ms |
Image
image/jpeg |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Sep_Oct_Specials_-_Menu_Ad_Card.webp
res.cloudinary.com/hpf2bgvwe/image/upload/v1787724224/media/00D2v000003QBB7EAO/ |
262 KB 263 KB |
62ms
61ms |
Image
image/webp |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Our_Values_Icons_V2_organically-grown-aloe-new.webp
res.cloudinary.com/hpf2bgvwe/image/upload/v1753778337/media/00d2v000003qbb7eao/ |
26 KB 27 KB |
66ms
65ms |
Image
image/webp |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Our_Values_Icons_V2_natural-botanical-new.webp
res.cloudinary.com/hpf2bgvwe/image/upload/v1753778339/media/00d2v000003qbb7eao/ |
22 KB 22 KB |
67ms
66ms |
Image
image/webp |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Our_Values_Icons_V2_cruelty-free-09-new.webp
res.cloudinary.com/hpf2bgvwe/image/upload/v1753778339/media/00d2v000003qbb7eao/ |
18 KB 18 KB |
68ms
67ms |
Image
image/webp |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Our_Values_Icons_V2_australian-made-07-new.webp
res.cloudinary.com/hpf2bgvwe/image/upload/v1753778340/media/00d2v000003qbb7eao/ |
18 KB 19 KB |
68ms
68ms |
Image
image/webp |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Our_Values_Icons_V2_non-toxic-new.webp
res.cloudinary.com/hpf2bgvwe/image/upload/v1753778338/media/00d2v000003qbb7eao/ |
13 KB 14 KB |
70ms
69ms |
Image
image/webp |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Our-Values-Icons-V2_pregnancy-safe-new.webp
res.cloudinary.com/hpf2bgvwe/image/upload/v1753778336/media/00d2v000003qbb7eao/ |
18 KB 18 KB |
75ms
74ms |
Image
image/webp |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
aloe-juice-gallery-original.webp
res.cloudinary.com/hpf2bgvwe/image/upload/v1753778728/media/00d2v000003qbb7eao/ |
122 KB 122 KB |
73ms
72ms |
Image
image/webp |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
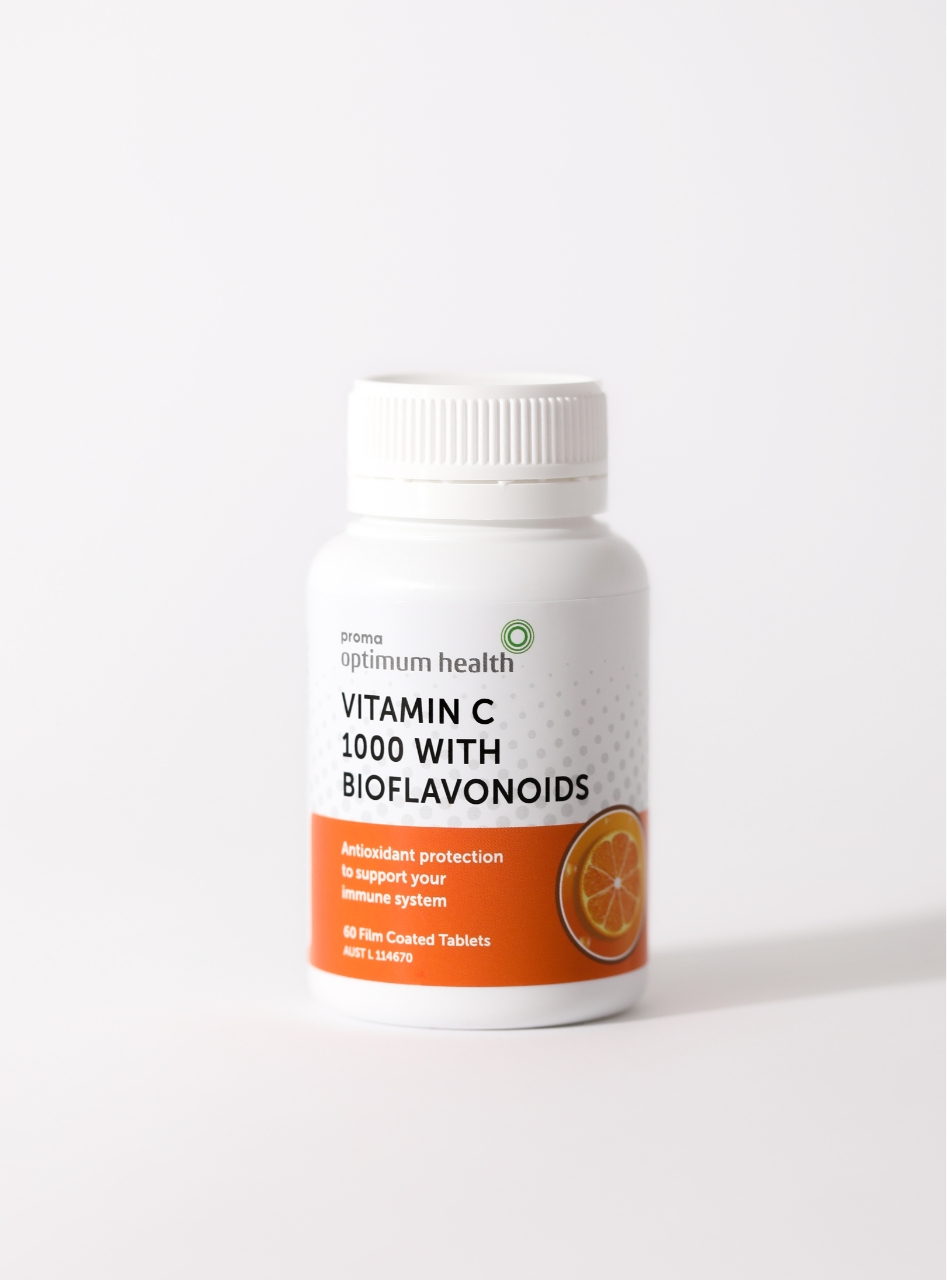
vitamin-c-21.jpg
res.cloudinary.com/hpf2bgvwe/image/upload/v1753772785/media/00d2v000003qbb7eao/ |
318 KB 319 KB |
76ms
75ms |
Image
image/jpeg |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
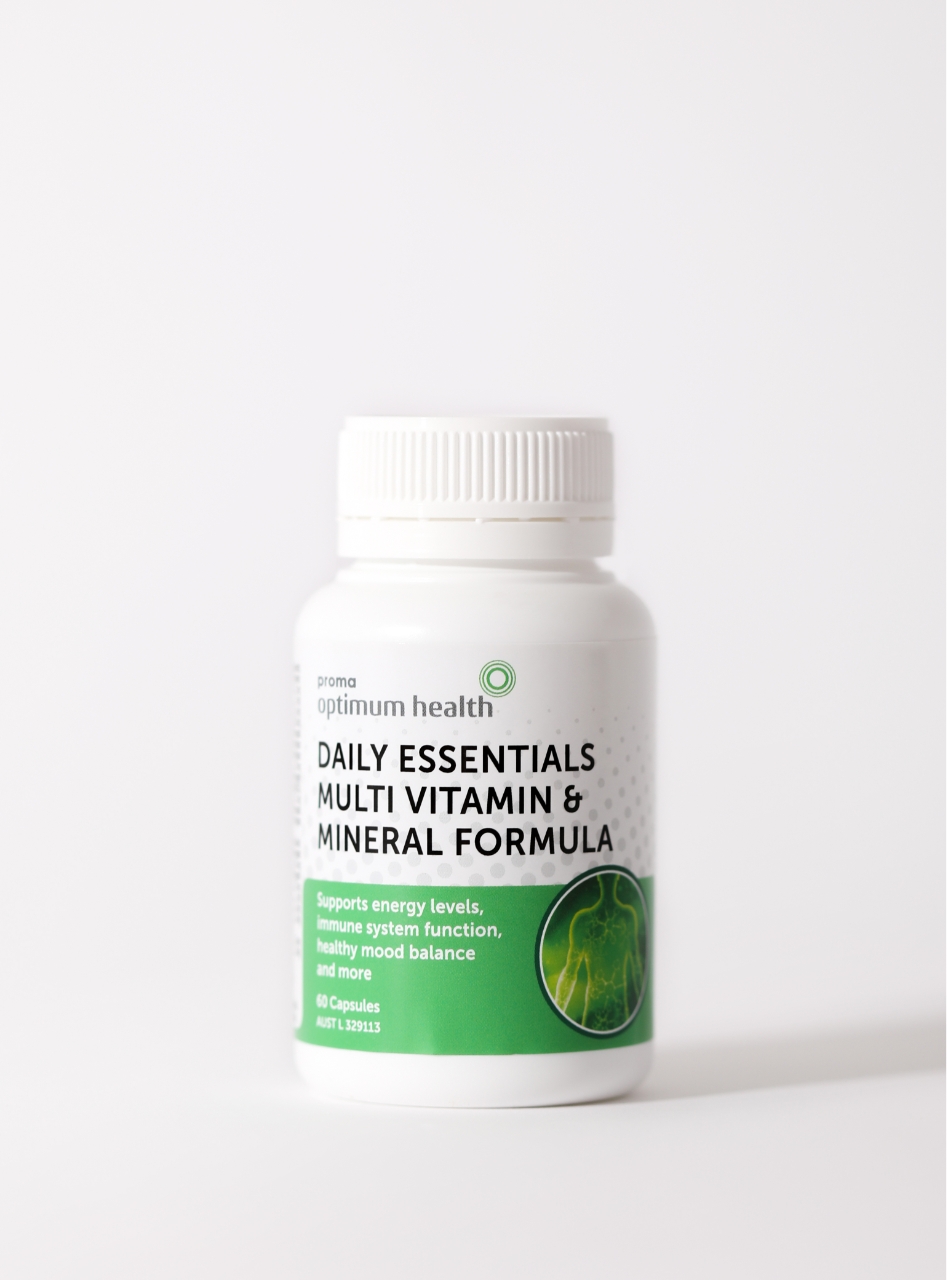
daily-essentials-21.jpg
res.cloudinary.com/hpf2bgvwe/image/upload/v1753772767/media/00d2v000003qbb7eao/ |
330 KB 331 KB |
82ms
82ms |
Image
image/jpeg |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
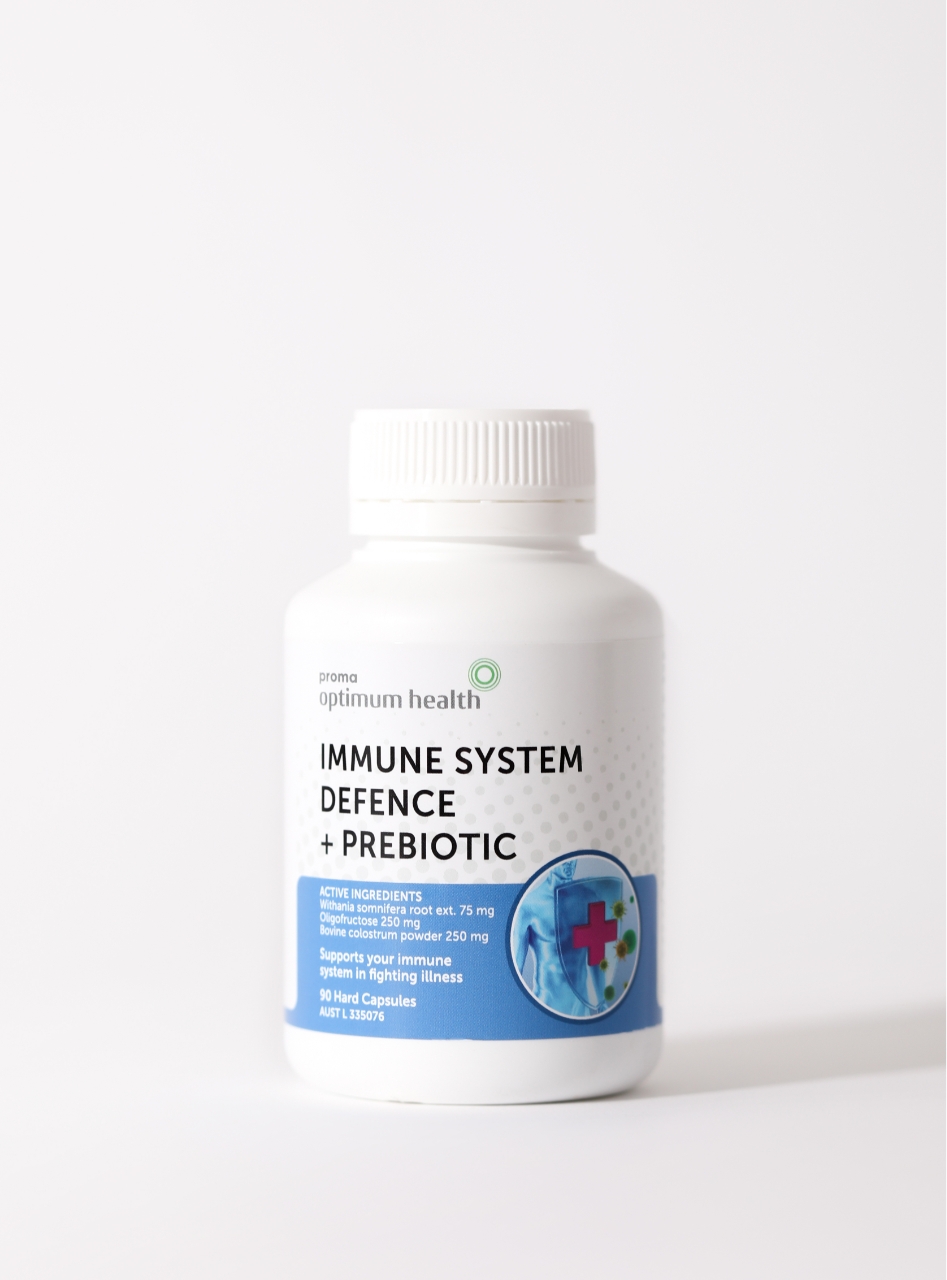
Immune-system-defense-21.jpg
res.cloudinary.com/hpf2bgvwe/image/upload/v1753772798/media/00d2v000003qbb7eao/ |
313 KB 314 KB |
90ms
89ms |
Image
image/jpeg |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
MBL8-icons-7.png
res.cloudinary.com/hpf2bgvwe/image/upload/v1753778854/media/00d2v000003qbb7eao/ |
9 KB 10 KB |
96ms
95ms |
Image
image/png |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
MBL8-icons-5.png
res.cloudinary.com/hpf2bgvwe/image/upload/v1753778853/media/00d2v000003qbb7eao/ |
6 KB 7 KB |
97ms
97ms |
Image
image/png |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
MBL8-icons-3.png
res.cloudinary.com/hpf2bgvwe/image/upload/v1753778851/media/00d2v000003qbb7eao/ |
5 KB 6 KB |
98ms
97ms |
Image
image/png |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
MBL8-icons-1.png
res.cloudinary.com/hpf2bgvwe/image/upload/v1753778847/media/00d2v000003qbb7eao/ |
11 KB 11 KB |
98ms
98ms |
Image
image/png |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET DATA |
200 OK |
truncated
/ |
281 B 0 |
Image
image/svg+xml |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
optimum-health-banner-image-v2-cropped.jpg
res.cloudinary.com/hpf2bgvwe/image/upload/v1753777864/media/00d2v000003qbb7eao/ |
240 KB 0 |
0ms
0ms |
Image
image/jpeg |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
optimum-health-tablets_assortment.jpg
res.cloudinary.com/hpf2bgvwe/image/upload/v1753773757/media/00d2v000003qbb7eao/ |
128 KB 0 |
0ms
0ms |
Image
image/jpeg |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET DATA |
200 OK |
truncated
/ |
221 B 0 |
Image
image/svg+xml |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
l
use.typekit.net/af/78aca8/00000000000000007735e60d/30/ |
29 KB 30 KB |
167ms
104ms |
Font
application/font-woff2 |
184.84.165.106 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Proma_Desktop_Image_V1_-_1024-opt.webp
res.cloudinary.com/hpf2bgvwe/image/upload/v1782974461/media/00D2v000003QBB7EAO/ |
130 KB 131 KB |
48ms
47ms |
Image
image/webp |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
OPTIONS H2 |
200 |
/
sessions.bugsnag.com/ Frame |
0 0 |
331ms
226ms |
Preflight
|
35.190.88.7 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
202 |
/
Show response
sessions.bugsnag.com/ |
21 B 131 B |
199ms
197ms |
XHR
application/json |
35.190.88.7 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
spinner.svg
Show response
ka-p.fontawesome.com/releases/v6.7.2/svgs/solid/ |
576 B 403 B |
27ms
27ms |
Fetch
image/svg+xml |
172.64.147.188 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
xmark.svg
Show response
ka-p.fontawesome.com/releases/v6.7.2/svgs/solid/ |
527 B 410 B |
36ms
35ms |
Fetch
image/svg+xml |
172.64.147.188 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
tag.svg
Show response
ka-p.fontawesome.com/releases/v6.7.2/svgs/solid/ |
452 B 408 B |
36ms
35ms |
Fetch
image/svg+xml |
172.64.147.188 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
gift.svg
Show response
ka-p.fontawesome.com/releases/v6.7.2/svgs/sharp-solid/ |
733 B 553 B |
46ms
46ms |
Fetch
image/svg+xml |
172.64.147.188 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
main.js
Show response
proma.global/cdn-cgi/challenge-platform/h/g/scripts/jsd/330e41bb475c/ Frame 44D1 Redirect Chain
|
21 KB 10 KB |
25ms
24ms |
Script
application/javascript |
104.21.8.240 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET DATA |
200 OK |
truncated
/ |
264 B 0 |
Image
image/svg+xml |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
200 |
a3a843446a1a7880
Show response
proma.global/cdn-cgi/challenge-platform/h/g/jsd/oneshot/330e41bb475c/0.6024444541248778:1789311912:hwZNqVLlQxWNC9GSgYrd1UwERKn3aTZhX4h_4l2qfU4/ Frame 44D1 |
0 647 B |
36ms
31ms |
XHR
text/plain |
104.21.8.240 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
js
Show response
www.googletagmanager.com/gtag/ |
558 KB 183 KB |
185ms
185ms |
Script
application/javascript |
142.251.42.104 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
fbevents.js
Show response
connect.facebook.net/en_US/ |
410 KB 108 KB |
98ms
41ms |
Script
application/x-javascript |
157.240.8.23 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
200 |
collect
www.google.com/ccm/ |
0 0 |
297ms
153ms |
Fetch
text/plain |
142.251.157.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
204 |
collect
ad.doubleclick.net/ccm/s/ |
0 0 |
302ms
154ms |
Fetch
text/html |
142.250.195.134 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
3594847624106051
Show response
connect.facebook.net/signals/config/ |
479 KB 135 KB |
317ms
317ms |
Script
application/x-javascript |
157.240.8.23 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
events
k6-e4e4123be8e54363900a90353991ca93.ecs.us-west-1.on.aws/ |
0 0 |
962ms
486ms |
Fetch
application/json |
54.177.251.2 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
200 |
/
Show response
www.facebook.com/tr/ Frame A832 |
0 20 B |
82ms
40ms |
Document
text/plain |
157.240.8.35 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
destination
Show response
www.googletagmanager.com/gtag/ |
598 KB 192 KB |
167ms
166ms |
Script
application/javascript |
142.251.42.104 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
collect
analytics.google.com/g/ |
0 0 |
379ms
172ms |
Fetch
text/plain |
216.239.34.181 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
collect
stats.g.doubleclick.net/g/ |
0 547 B |
854ms
438ms |
Ping
text/plain |
74.125.200.157 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
ga-audiences
www.google.com.au/ads/ |
42 B 63 B |
299ms
151ms |
Image
image/gif |
172.217.25.163 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
/
Show response
googleads.g.doubleclick.net/pagead/viewthroughconversion/11291826309/ |
6 KB 3 KB |
310ms
163ms |
Script
text/javascript |
142.250.195.130 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
200 |
/
www.google.com/rmkt/collect/11291826309/ |
0 0 |
153ms
153ms |
Fetch
text/html |
142.251.157.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
200 |
collect
www.google.com/ccm/ |
0 0 |
153ms
153ms |
Fetch
text/plain |
142.251.157.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
/
www.google.com/pagead/1p-user-list/11291826309/ |
42 B 64 B |
162ms
162ms |
Image
image/gif |
142.251.157.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
/
www.google.com.au/pagead/1p-user-list/11291826309/ |
42 B 64 B |
169ms
169ms |
Image
image/gif |
172.217.25.163 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
204 |
rum
Show response
proma.global/cdn-cgi/ |
0 444 B |
33ms
32ms |
XHR
text/plain |
104.21.8.240 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
globe-solid.svg
res.cloudinary.com/hirviubsa/image/upload/v1616979960/media/ |
968 B 1020 B |
49ms
48ms |
Other
image/svg+xml |
2.18.224.45 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
bootstrap.min.js
proma.my.site.com/ESWCareTeamWebChat1707799953248/assets/js/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||




































































Failed requests
These URLs were requested, but there was no response received. You will also see them in the list above.
- Domain
- proma.my.site.com
- URL
- https://proma.my.site.com/ESWCareTeamWebChat1707799953248/assets/js/bootstrap.min.js
Verdicts & Comments Add Verdict or Comment
114 JavaScript Window variables
Go Pro
Only in urlscan Pro
Inspect and pivot on JavaScript variables, identifiers, and other key site metadata data with urlscan Pro. Reveal and search on client-side frameworks, runtime variables, and custom values.
Click for more information
Free trials of urlscan Pro are available.
These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.
object| 0 object| 1 object| Rails boolean| _rails_loaded object| StoreConnect object| dataLayer object| FontAwesomeKitConfig function| $ function| jQuery string| currentUserAccountTypeHeaderJs object| promaLineItems boolean| bagContainsBundledProduct function| scrollPageToPos function| cleanHtmlEntities object| url object| params function| getRandomIntInclusive string| currentURL string| currentPage string| currentStore string| CURRENTSTORE function| createAccordion function| createAccordionItem function| createProductElement function| filterProductsByGeo function| createFeaturedProducts function| createBestSellersView function| toArray function| scrollFunction1 function| offset function| embedVideo function| embedVideo2 function| createDebugContainer function| createAccordionVariantPageOld function| embedVideovariantPages function| introTextDisplay function| createAccordionTabsBodyTemplate2 function| wrapElAll function| wrapEl function| wrapElements function| subStringHeading function| badge function| setCookie function| getCookie function| validateEmail function| promaRotateText function| promaCreateTabbablePanes function| validateAustralianPhoneNumber function| detectDeviceAndBrowser function| getHeightWithMargin function| embedVideoWithMessage function| acCleanUp function| acManageAjax function| acDeleteAllProducts function| acUpdateProduct function| acDeleteProduct function| acDeleteProductDebounced function| gtag number| countDownDate function| updateElement function| updateCountdown number| x function| on function| off function| check object| namespaces object| featuredProductsArray string| currentStorePath string| productId string| productName string| productPath string| productImages string| productImageUrl object| multiProductReviewsIdsArray object| howToUseVideoUrl object| contentObj object| promaPerformanceAdContainer object| promaPerformanceAd function| footerBlurb function| initEmbeddedMessaging string| styles function| CaptchaCallback function| CaptchaCallbackPpf object| aloeJourney object| ___FONT_AWESOME___ object| fontawesome-pro-shims object| FontAwesomeConfig object| FontAwesome function| initializeFormPpf function| getUserDataPpf function| isMoreThanOneYearFromTodayPpf function| isMoreThanSixMonthsAgo function| checkQualification function| setUpFormSubmissionPpf function| handleFormSubmitPpf function| handlePopupDisplayPpf function| handleIframeLoadPpf function| savePromoCodePpf function| popupShopPpf function| resetFormPpf function| closeAllPromaAlerts number| uidEvent object| bootstrap object| __cfBeacon object| bugsnagClient object| __bugsnag_fetch_tracker__ object| __bugsnag_xhr_tracker__ object| google_tag_manager object| google_tag_data function| fbq function| _fbq function| onYouTubeIframeAPIReady object| gaGlobal object| GooglebQhCsO9 Cookies
Go Pro
Only in urlscan Pro
Review, search, and pivot on browser cookies and persistence site data to see how a site tracks users and keeps sessions alive across visits.
Click for more information
Free trials of urlscan Pro are available.
Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.
| Domain/Path | Expires | Name / Value | |||
|---|---|---|---|---|---|
| .proma.global/ | 1970-01-22 02:37:54 |
Name: sc_token Value: eyJfcmFpbHMiOnsibWVzc2FnZSI6ImV5SjBiMnRsYmlJNkltTm1PR0prTkdNeUxUVTVOalF0TkRBeFlTMWhNV1UyTFdRellXWm1aVFkyT1RjNU9DSXNJbXh2WjJkbFpGOXBiaUk2Wm1Gc2MyVjkiLCJleHAiOm51bGwsInB1ciI6ImNvb2tpZS5zY190b2tlbiJ9fQ%3D%3D--292a8f058756d509f70032223a9ce7f9aa7137f0 |
|||
| proma.global/ | 1969-12-31 23:59:59 |
Name: store_connect_session Value: bdee45b4fced6b0c4b11b4777686bb55 |
|||
| .proma.global/ | 1970-01-22 01:47:30 |
Name: cf_clearance Value: D5Wm1KcDUKsRHJGm4YUI0b9vzCwWWtM6dJFkwaGfQy8-1789314159-1.2.1.1-hK4EsrG2R3ef43QywF0MPSw.QbvjbQ3PfDPXV0pUdlqSLnrOc316yrb8knICuzNGZhLdKmz6XYrL6yry3.g6REVLfb_Tq8r9TUmZvzXKPtDwFU9P.Wr_NatdFBRGcbpOkdO1XzQ5jZBP61YtuZHNuKjXD_IeIFzO5I3MM4CBQY3Qkoih8HddmDGIdII9IW2gUjQd3XMqYaFimBu3vzFNxNlcD22zC5DUWqGa5y5HJhBPWGcJz8Vo39CRhtafsF.J1LJ5hYebINsgZ5f0J.m_p.NnbBO5dhn0ue5XcVLUawr8yAvX9j3ICYbX4TcE86UV2nzQ6ZeAejBRL9FAjkGutMNz8LeGnHaPStnT_zWuM8g |
|||
| .proma.global/ | 1970-01-21 19:11:30 |
Name: _gcl_au Value: 1.1.2049428659.1789314161 |
|||
| .proma.global/ | 1970-01-21 19:11:30 |
Name: _fbp Value: fb.1.1789314161300.222687117722588168 |
|||
| .proma.global/ | 1970-01-22 02:37:54 |
Name: _ga_RQZWRRWJGK Value: GS2.1.s1789314161$o1$g0$t1789314161$j60$l0$h1241318155 |
|||
| .proma.global/ | 1970-01-22 02:37:54 |
Name: _ga Value: GA1.1.562900882.1789314161 |
|||
| .facebook.com/ | 1970-01-21 19:11:30 |
Name: fr Value: 0b3r3wdPUrGYHc53f..BqpsRx...1.0.BqpsRx.AWfOOgYcHt5p9atloLQJuVZkOdk |
|||
| .doubleclick.net/ | 1970-01-21 17:01:55 |
Name: test_cookie Value: CheckForPermission |
1 Console Messages
A page may trigger messages to the console to be logged. These are often error messages about being unable to load a resource or execute a piece of JavaScript. Sometimes they also provide insight into the technology behind a website.
| Source | Level | URL Text |
|---|
Security Headers
This page lists any security headers set by the main page. If you want to understand what these mean and how to use them, head on over to this page
| Header | Value |
|---|---|
| Strict-Transport-Security | max-age=63072000; includeSubDomains |
| X-Content-Type-Options | nosniff |
| X-Frame-Options | SAMEORIGIN |
| X-Xss-Protection | 0 |
Indicators
This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.
ad.doubleclick.net
analytics.google.com
cdn.jsdelivr.net
cdnjs.cloudflare.com
code.jquery.com
connect.facebook.net
googleads.g.doubleclick.net
k6-e4e4123be8e54363900a90353991ca93.ecs.us-west-1.on.aws
ka-p.fontawesome.com
kit.fontawesome.com
p.typekit.net
proma.global
proma.my.site.com
promaoptimumhealth.com.au
res.cloudinary.com
sessions.bugsnag.com
static.cloudflareinsights.com
stats.g.doubleclick.net
use.typekit.net
www.facebook.com
www.google.com
www.google.com.au
www.googletagmanager.com
proma.my.site.com
104.16.79.73
104.17.208.5
104.17.25.14
104.21.8.240
142.250.195.130
142.250.195.134
142.251.157.119
142.251.42.104
151.101.1.155
157.240.8.23
157.240.8.35
172.217.25.163
172.64.147.188
172.67.202.234
184.84.165.106
2.18.224.45
216.239.34.181
23.46.179.155
35.190.88.7
54.177.251.2
74.125.200.157
00ff98ab1ce128500818c945c8fc6c096032ebc240450db6f80e1a7506ee62d0
0225bdd21ee73b2942003e83bbe7caac4ec6aa607dacc4f1b23156a4976387f8
036c9c1d85d1a6e42fc3eecfb7fe6451d05d8319a7649f86ca3b25173dc1df9b
08c4fd72f9d96a7aa554510dff2c293973b1b092dff1b9b282bce9111b50ef41
0ba7c0356149946bf0642fab4ef85b95e7090f6f785d0fb84323d0c442e5190a
0c22b03fe93f41d23da272cf7fe19caa480973ff03c4ab7edade16e6397838c1
0c7178cc6ca34fb18e30f070a5e7a1c287b2d7ccfcba2cfdf06e0f46eda55740
11f8de7ac1d1b5ab8fda03417402becd304e69cf81b315cce84bdd003674f6e6
156639641d2acc88b7449dcbc97dfcb35c0aed3c7ba46074682ed4004cf4838b
1591630d40913bf9c479c5d01517661fe15736f752e02deff76d99e6a4e0bc2a
1888487815750370a14f0da9c7625226afb60637e25508bd03c738d659e32480
1c0ff118a4290c99f39c90abb38703a866e47251b23cca20266c69c812ccafeb
1cb01138df237c0942f574471c3f9e2284687df5f7fa8e58615d7eae3ae363a7
1fe2bb5390a75e5d61e72c107cab528fc3c29a837d69aab7d200e1dbb5dcd239
20789d23760268f339a76d9f38087d17a6cab84f1f40ad7cf425decb9c13075c
2734df22b97c82bbda7d0c2bc572e5e9811c42cbf82b46611bcac289a159bc7a
2846b56de194fb153d3cfe1c541fca5891761f3270096fb68432543ed4eb4e93
2c4a1efd964518c4e68172b0cd61c688446b6c32ad90883d086955f3284c680a
3521021a2e875fbc52ae82e2a3fea5024d507bbc919f504ca8521292c3fe14d3
354e316702c3b55865551a0a602ec2790fb3713f92c840c22475e41284776e16
45620fdba7be84d26213761da71ac7af5ae8bd7da7f3fc3bdf6cf4f2733dac11
4654967259a0f42e3703fbc474c0250e4586825a92b47d1d42d8578a000077fb
4972a9ae1e9dabed960916ec25ecf35aa56550c3678278d65f3726855ab1da1a
50ad448a8a5720bf8a5617db15af31ae60163de06331576f60c6244c012ffc72
659bea98a59fb8cc403952de7e1190508f773c2d82a4648b660b9e92e4304455
6707be7eb86fbace9ecb81452bcf4a4a4695c5802c69d1566434c9b97285662b
69c0ffa545cd95e6295e39c2728706027437d4ec5592b6bf9bd1717d3e2842a7
6afea3c23c4f7b6599acff42ce6124ab617ce62c5f18b5b9b8e69d34358f784c
6b9a75570471bdd0556205ac2a1869355482faf513e6ab8f4f1b702b1d51189c
6e9c75e0d0775891ec7b2d49b35e2ea490a28ddc58f8082223db07b154ff44df
72262baf381a5e32c19311219faec4669e7e1df0fe20f2a557a4cd7a4e4e95ea
75f3938b3a8d37703712dcefcb913d12d2f16b066233150f78dbb2eff87ef4eb
77614855e087fe95432057ec6133e07e374d282b0f3c7efc85d02913b0db98af
79d3c7bf3ef1c93ed78b8ba6c8c1d8ba712458005950403dd9e5263059fca8c7
7e3d79329fd129a886c254ecc66ef53c5370f1f389d4d0996ceccd1c5448e8a6
7e8218e8db9a8304d8a9cd4e15c73a94606fd8b7fabf1f61e4a3ea8252324551
7edf938fd09d0b0554ac2a3568e0d66a85be48ef88a05b8dee99ad60d69a9871
829516b45178186dee37e08f262bd3b5e21c0d6ff97369c6c871c90a91208187
8393a74bde8b0f7928195e21dacb05fcd8e024d5356aa7825a1cf9e3e99424ea
89fcfb210a2067c0b348ce5c15c8edb067987d3601d491640def1a31777eb4f8
8aca02e5349f6d238cc6ca67df59b2f8a2ac79ea5fa8512726b52dc4358684b1
949aeae32555f7b3778cc85d65c4bf7b0135edd78f70bfb791efe6932276337d
9520018fa5d81f4e4dc9d06afb576f90cbbaba209cfcc6cb60e1464647f7890b
9767790468cc10d794df7ddf82828d58484b96a2e4e4ba869158495783be81a0
9896244240fb1f0d140378ed6bca99c9c9958ca85f43b1c6945a3049cfa939e1
9ba59c2fd301dbbc6c6a22938475bc54fce770bc15aa1beb0e54d40891d3ea36
a2eed8b33b25f6d950b20edfa43abb6c06d31fcdeac0147cd4135c85cf53fe36
a33128c94dd3c425bc3f4a9ba389a1f3d7a75233e8cb788ea80f8f43a3d68423
b642d4ccb77d6d45c146d6f493a6d6cce37c267a40152fffd244fe1caf92b5a5
b99f3ed4cfb0313a984ae441209de40e81af6eaa3281fb82d0eec6b3b2048ccc
bd7f7c0f0d2c857c1981dae1c9224ba44a6e0c8baff8d2b0b30362694235b3ec
beef1b5416b61a2eb8a2386234c3792e16b122ac8a71abdd21b5be54f2090f16
c0bcf7898fdc3b87babca678cd19a8e3ef570e931c80a3afbffcc453738c951a
c3b972609b7343e788b0beccb33c7d29628e2952b579a23cce0729c31e8bc307
c3f6dbbb696a62e3fa29e3f92a8e877841955eb8a0c058e77c444382bbac1419
c40d4cf34a565e069d53d1f15ce5ef49948b4c9889704bb82998c7e887d9151d
c4d04d2b6a041dde11c80d8332f983a58c1031c663ab4f42230899cb82adf4a7
ca88a775ab67ee3e7bd79e41537cb6544eafb895bf4151bfa3c1876291934224
cb79a5617159e549b7e9b4e4e39312da6ccae89cba2e8f00199bd3f9a5cb0e55
cffe18b1d2b3f9a8f18f1f254fc2a3857a5016cf1cfaa08d526bb15d3036380c
d0b683a4b64e33c01608d02654f60c80fd8411f44b27e8fa6d76231850bcdf0a
d47ae7e60195ef790f63510716b72c7c0f7f2abac8d6eb3708dab02827e7fdbe
e21aa5b0d3fd28cebed9e03c5544f4924e11b0c453792ed018720cf8c679b0b6
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
e533b43ecfe2717118daae24c69b37946b83644981b5b04c017bb76c1e4c3699
e55ee0cea4fb9ce56af422bf68c03911dfe9923a54ba50a4e21ba740106fed0f
e8f2ac736b5c7b7874ec33865131808e33ea2afa1732a4cbca7b87030a564cbe
ea604bf4dc3be3aff3b94989700fa1cdd97c00a388a8a036a8785eca1da84a0d
ece2e95e0833a3ca202d786151532f388ff73be29ea66334534ed1fa597dfd7d
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
f23c3b8f196f65bff4e9029e776c0e6fb47a18c19415c9bc0f40ec276f019087
f5c490c1b3bedef83a836f8a27b7f722e6c131524b97a4146ad8015005e1cd82
fcdd146a655931f6a64fa67e57edef1a80ef58ed21cd89ea8cc09d0278f459d1
ff443f27407387bc3897ab768cd1e14ba4329039bff3077a9ad0ba05748f3b3d