Summary

This website contacted 71 IPs in 8 countries across 50 domains to perform 240 HTTP transactions. The main IP is 109.201.135.99, located in Netherlands and belongs to NFORCE NForce Entertainment B.V., NL. The main domain is footyroom.co. 8yr old
TLS certificate: Issued by YR2 on August 18th 2026. Valid for: 3mo.
This is the only time footyroom.co was scanned on urlscan.io!

Domain & IP information

IP Address AS Autonomous System
40 109.201.135.99 109.201.135.99 43350 (NFORCE NF...) (NFORCE NForce Entertainment B.V.)
8 104.18.3.78 104.18.3.78 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
2 2a00:1450:400... 2a00:1450:4001:c15::66 15169 (GOOGLE) (GOOGLE - Google LLC)
3 2606:4700:440... 2606:4700:4405::6812:21f7 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
2 2a00:1450:400... 2a00:1450:4001:c15::61 15169 (GOOGLE) (GOOGLE - Google LLC)
4 2a00:1450:400... 2a00:1450:4001:c0f::5f 15169 (GOOGLE) (GOOGLE - Google LLC)
10 142.251.127.156 142.251.127.156 15169 (GOOGLE) (GOOGLE - Google LLC)
1 151.101.1.195 151.101.1.195 54113 (FASTLY) (FASTLY - Fastly)
1 104.17.25.14 104.17.25.14 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
2 104.16.225.240 104.16.225.240 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
6 35.244.144.25 35.244.144.25 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC)
11 185.167.98.14 185.167.98.14 41436 (CloudWebM...) (CloudWebManage-EU Kamatera Inc)
1 13.33.187.36 13.33.187.36 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
4 172.64.144.166 172.64.144.166 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
2 178.162.196.143 178.162.196.143 28753 (LEASEWEB-...) (LEASEWEB-DE-FRA-10 Leaseweb Deutschland GmbH)
2 2a00:1450:400... 2a00:1450:4001:c13::8a 15169 (GOOGLE) (GOOGLE - Google LLC)
5 2001:4860:482... 2001:4860:4826:400:: 15169 (GOOGLE) (GOOGLE - Google LLC)
4 2a00:1450:400... 2a00:1450:4001:c15::77 15169 (GOOGLE) (GOOGLE - Google LLC)
4 142.250.154.94 142.250.154.94 15169 (GOOGLE) (GOOGLE - Google LLC)
12 142.251.110.100 142.251.110.100 15169 (GOOGLE) (GOOGLE - Google LLC)
1 95.211.37.134 95.211.37.134 60781 (LEASEWEB-...) (LEASEWEB-NL-AMS-01 LeaseWeb Netherlands B.V.)
2 143.204.173.87 143.204.173.87 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
3 2606:4700:10:... 2606:4700:10::ac42:ab85 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
2 143.204.181.10 143.204.181.10 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 2 142.251.13.154 142.251.13.154 15169 (GOOGLE) (GOOGLE - Google LLC)
1 2a00:1450:400... 2a00:1450:4001:c21::94 15169 (GOOGLE) (GOOGLE - Google LLC)
1 142.251.150.4 142.251.150.4 15169 (GOOGLE) (GOOGLE - Google LLC)
4 142.251.156.119 142.251.156.119 15169 (GOOGLE) (GOOGLE - Google LLC)
1 2a00:1450:400... 2a00:1450:4001:c17::77 15169 (GOOGLE) (GOOGLE - Google LLC)
1 2a00:1450:400... 2a00:1450:4001:c13::84 15169 (GOOGLE) (GOOGLE - Google LLC)
1 2a00:1450:400... 2a00:1450:4001:c17::5e 15169 (GOOGLE) (GOOGLE - Google LLC)
2 2600:9000:26e... 2600:9000:26e8:a200:11:a9de:ec0:93a1 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
2 2001:4860:484... 2001:4860:4845:400:: 15169 (GOOGLE) (GOOGLE - Google LLC)
11 2606:4700:10:... 2606:4700:10::ac42:948c 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
7 142.251.14.149 142.251.14.149 15169 (GOOGLE) (GOOGLE - Google LLC)
2 34.36.200.111 34.36.200.111 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC)
1 2606:4700:10:... 2606:4700:10::6814:14bd 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
1 18.245.31.123 18.245.31.123 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
4 2600:9000:201... 2600:9000:2013:ac00:4:b37b:9440:93a1 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
4 2a00:1450:400... 2a00:1450:4001:c15::5f 15169 (GOOGLE) (GOOGLE - Google LLC)
4 2600:9000:26e... 2600:9000:26e8:e000:11:a9de:ec0:93a1 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 2600:9000:225... 2600:9000:2251:f600:15:c08e:ec40:93a1 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 2600:9000:28e... 2600:9000:28eb:cc00:12:a1d3:a3c0:93a1 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 35.244.174.68 35.244.174.68 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC)
1 34.98.64.218 34.98.64.218 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC)
1 35.201.104.135 35.201.104.135 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC)
1 2600:9000:208... 2600:9000:208a:a00:18:f839:ac80:21 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 2600:9000:20e... 2600:9000:20e8:fa00:3:c079:7fc0:93a1 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 2 34.111.113.62 34.111.113.62 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC)
1 103.231.98.107 103.231.98.107 62713 (AS-PUBMATIC) (AS-PUBMATIC - PubMatic)
1 69.173.144.165 69.173.144.165 26667 (RUBICONPR...) (RUBICONPROJECT - Magnite)
1 1 2606:4700:10:... 2606:4700:10::ac42:a677 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
5 2606:4700:10:... 2606:4700:10::6814:2396 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
1 2606:4700:10:... 2606:4700:10::ac42:a937 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
1 13.226.244.59 13.226.244.59 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 2.16.241.214 2.16.241.214 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.)
6 142.251.20.154 142.251.20.154 15169 (GOOGLE) (GOOGLE - Google LLC)
2 2a00:1450:400... 2a00:1450:4001:c25::95 15169 (GOOGLE) (GOOGLE - Google LLC)
2 2a04:4e42:400... 2a04:4e42:400::485 54113 (FASTLY) (FASTLY - Fastly)
8 135.125.170.108 135.125.170.108 16276 (OVH OVH SAS) (OVH OVH SAS)
5 52.223.40.198 52.223.40.198 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 2001:4860:480... 2001:4860:4802:36::181 15169 (GOOGLE) (GOOGLE - Google LLC)
1 2a00:1450:400... 2a00:1450:4001:c21::9a 15169 (GOOGLE) (GOOGLE - Google LLC)
4 135.125.170.28 135.125.170.28 16276 (OVH OVH SAS) (OVH OVH SAS)
1 63.180.245.66 63.180.245.66 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 52.223.6.21 52.223.6.21 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
2 34.36.209.34 34.36.209.34 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC)
2 2602:803:c003... 2602:803:c003:200::21 26667 (RUBICONPR...) (RUBICONPROJECT - Magnite)
2 46.228.165.115 46.228.165.115 56396 (Amobee NE...) (Amobee NEXXEN GROUP LTD)
1 35.207.108.208 35.207.108.208 15169 (GOOGLE) (GOOGLE - Google LLC)
1 2607:f8b0:402... 2607:f8b0:4023:2007::5e 15169 (GOOGLE) (GOOGLE - Google LLC)
240 71
Apex Domain
Subdomains
Transfer
38 footyroom.co
footyroom.co 8yr old
cdn.footyroom.co 7yr old
213 KB
21 doubleclick.net 1 redirects
securepubads.g.doubleclick.net — Cisco Umbrella Rank: 352 10yr old
googleads.g.doubleclick.net — Cisco Umbrella Rank: 68 10yr old
static.doubleclick.net — Cisco Umbrella Rank: 287 10yr old
ad.doubleclick.net — Cisco Umbrella Rank: 129 10yr old
stats.g.doubleclick.net — Cisco Umbrella Rank: 156 10yr old
274 KB
16 google.com
fundingchoicesmessages.google.com — Cisco Umbrella Rank: 734 8yr old
www.google.com — Cisco Umbrella Rank: 4 14yr old
analytics.google.com — Cisco Umbrella Rank: 146 9yr old
105 KB
11 ad-delivery.net
ad-delivery.net — Cisco Umbrella Rank: 1519 9yr old
2 KB
11 scalibur.io
srv.scalibur.io — Cisco Umbrella Rank: 16395 1yr old
537 KB
10 googleapis.com
ajax.googleapis.com — Cisco Umbrella Rank: 605 10yr old
fonts.googleapis.com — Cisco Umbrella Rank: 43 10yr old
jnn-pa.googleapis.com — Cisco Umbrella Rank: 348 5yr old
imasdk.googleapis.com — Cisco Umbrella Rank: 621 10yr old
535 KB
9 id5-sync.com
cdn.id5-sync.com — Cisco Umbrella Rank: 904 7yr old
id5-sync.com — Cisco Umbrella Rank: 593 9yr old
40 KB
9 p7cloud.net
silo60.p7cloud.net — Cisco Umbrella Rank: 51461 1yr old
ua.p7cloud.net — Cisco Umbrella Rank: 30644 3yr old
location.p7cloud.net — Cisco Umbrella Rank: 30610 3yr old
lal.p7cloud.net — Cisco Umbrella Rank: 28664 3yr old
175 KB
9 youtube.com
www.youtube.com — Cisco Umbrella Rank: 108 10yr old
984 KB
9 nitropay.com
s.nitropay.com — Cisco Umbrella Rank: 34917 8yr old
floors.nitropay.com — Cisco Umbrella Rank: 38857 2yr old
244 KB
6 adsrvr.org
match.adsrvr.org — Cisco Umbrella Rank: 468 10yr old
direct.adsrvr.org — Cisco Umbrella Rank: 1340 9yr old
815 B
6 googlesyndication.com
pagead2.googlesyndication.com — Cisco Umbrella Rank: 119 10yr old
46 KB
6 gstatic.com
fonts.gstatic.com — Cisco Umbrella Rank: 31 10yr old
www.gstatic.com — Cisco Umbrella Rank: 9 10yr old
csi.gstatic.com — Cisco Umbrella Rank: 561 10yr old
104 KB
5 ad.gt
a.ad.gt — Cisco Umbrella Rank: 2576 10yr old
id.hadron.ad.gt — Cisco Umbrella Rank: 2457 4yr old
3 KB
5 nit.ro
t.nit.ro — Cisco Umbrella Rank: 33309 3yr old
5 ytimg.com
i.ytimg.com — Cisco Umbrella Rank: 124 10yr old
740 KB
4 eu-1-id5-sync.com
lb.eu-1-id5-sync.com — Cisco Umbrella Rank: 1034 4yr old
1 KB
4 geoedge.be
rumcdn.geoedge.be — Cisco Umbrella Rank: 2137 8yr old
109 KB
4 btloader.com
btloader.com — Cisco Umbrella Rank: 1339 6yr old
cdn.btloader.com — Cisco Umbrella Rank: 1859 2yr old
cdn.api.btloader.com — Cisco Umbrella Rank: 1868 8mo old
48 KB
4 confiant-integrations.net
cdn.confiant-integrations.net — Cisco Umbrella Rank: 2172 4yr old
467 KB
3 rubiconproject.com
pixel.rubiconproject.com — Cisco Umbrella Rank: 597 10yr old
fastlane.rubiconproject.com — Cisco Umbrella Rank: 823 10yr old
1 KB
3 amazon-adsystem.com
c.amazon-adsystem.com — Cisco Umbrella Rank: 557 13yr old
config.aps.amazon-adsystem.com — Cisco Umbrella Rank: 1041 4yr old
99 KB
3 traffmovie.com
cdn.traffmovie.com — Cisco Umbrella Rank: 177164 10mo old
z.cdn.traffmovie.com — Cisco Umbrella Rank: 189042 10mo old
20 KB
3 privacymanager.io
ats-wrapper.privacymanager.io — Cisco Umbrella Rank: 2142 5yr old
geo.privacymanager.io — Cisco Umbrella Rank: 1949 6yr old
41 KB
3 cleverwebserver.com
scripts.cleverwebserver.com — Cisco Umbrella Rank: 17797 5yr old
ui.cleverwebserver.com — Cisco Umbrella Rank: 18569 5yr old
call.cleverwebserver.com — Cisco Umbrella Rank: 18754 4yr old
30 KB
2 unrulymedia.com
targeting.unrulymedia.com — Cisco Umbrella Rank: 1022 10yr old
202 B
2 media.net
prebid.media.net — Cisco Umbrella Rank: 1302 8yr old
571 B
2 jsdelivr.net
cdn.jsdelivr.net — Cisco Umbrella Rank: 281 14yr old
1 KB
2 2mdn.net
s0.2mdn.net — Cisco Umbrella Rank: 547 10yr old
17 KB
2 tapad.com 1 redirects
pixel.tapad.com — Cisco Umbrella Rank: 696 10yr old
1 KB
2 dns-finder.com
ab.dns-finder.com — Cisco Umbrella Rank: 1760 1yr old
233 B
2 google-analytics.com
www.google-analytics.com — Cisco Umbrella Rank: 83 14yr old
21 KB
2 footyroom.com
images.footyroom.com 9yr old
7 KB
2 getclicky.com
static.getclicky.com — Cisco Umbrella Rank: 24361 11yr old
in.getclicky.com — Cisco Umbrella Rank: 22415 10yr old
6 KB
2 googletagmanager.com
www.googletagmanager.com — Cisco Umbrella Rank: 46 14yr old
291 KB
1 minutemedia-prebid.com
hb.minutemedia-prebid.com — Cisco Umbrella Rank: 6454 5yr old
90 B
1 sharethrough.com
btlr.sharethrough.com — Cisco Umbrella Rank: 2203 10yr old
119 B
1 fastclick.net
secure.cdn.fastclick.net — Cisco Umbrella Rank: 1696 14yr old
22 KB
1 crwdcntrl.net
tags.crwdcntrl.net — Cisco Umbrella Rank: 1096 14yr old
14 KB
1 hadronid.net 1 redirects
cdn.hadronid.net — Cisco Umbrella Rank: 2145 4yr old
312 B
1 pubmatic.com
image6.pubmatic.com — Cisco Umbrella Rank: 962 10yr old
193 B
1 cloudfront.net
d3j8vl19c1131u.cloudfront.net — Cisco Umbrella Rank: 17263 2yr old
284 B
1 ml314.com
vi.ml314.com — Cisco Umbrella Rank: 8420 5yr old
358 B
1 openx.net
us-u.openx.net — Cisco Umbrella Rank: 714 10yr old
273 B
1 rlcdn.com
idsync.rlcdn.com — Cisco Umbrella Rank: 766 10yr old
79 B
1 ggpht.com
yt3.ggpht.com — Cisco Umbrella Rank: 369 10yr old
5 KB
1 cloudflare.com
cdnjs.cloudflare.com — Cisco Umbrella Rank: 282 13yr old
14 KB
1 angularjs.org
code.angularjs.org — Cisco Umbrella Rank: 115529 10yr old
4 KB
0 smartadserver.com Failed
ssb-global.smartadserver.com Failed 4yr old
0 adnxs.com Failed
ib.adnxs.com Failed 10yr old
240 50
Domain Requested by
25 cdn.footyroom.co footyroom.co
cdn.footyroom.co
14 fundingchoicesmessages.google.com footyroom.co
cdn.confiant-integrations.net
14 footyroom.co footyroom.co
ajax.googleapis.com
cdnjs.cloudflare.com
11 ad-delivery.net btloader.com
11 srv.scalibur.io s.nitropay.com
cdn.confiant-integrations.net
srv.scalibur.io
10 securepubads.g.doubleclick.net footyroom.co
s.nitropay.com
securepubads.g.doubleclick.net
cdn.confiant-integrations.net
9 www.youtube.com ajax.googleapis.com
www.youtube.com
8 id5-sync.com srv.scalibur.io
8 s.nitropay.com footyroom.co
s.nitropay.com
cdn.confiant-integrations.net
7 ad.doubleclick.net btloader.com
6 pagead2.googlesyndication.com cdn.confiant-integrations.net
securepubads.g.doubleclick.net
6 silo60.p7cloud.net s.nitropay.com
cdn.confiant-integrations.net
5 match.adsrvr.org srv.scalibur.io
5 t.nit.ro s.nitropay.com
5 i.ytimg.com footyroom.co
www.youtube.com
4 lb.eu-1-id5-sync.com srv.scalibur.io
4 id.hadron.ad.gt srv.scalibur.io
4 imasdk.googleapis.com cdn.confiant-integrations.net
4 rumcdn.geoedge.be cdn.confiant-integrations.net
4 fonts.gstatic.com fonts.googleapis.com
www.youtube.com
4 cdn.confiant-integrations.net s.nitropay.com
cdn.confiant-integrations.net
3 ajax.googleapis.com footyroom.co
2 targeting.unrulymedia.com srv.scalibur.io
2 fastlane.rubiconproject.com srv.scalibur.io
2 prebid.media.net srv.scalibur.io
2 cdn.jsdelivr.net srv.scalibur.io
2 s0.2mdn.net cdn.confiant-integrations.net
2 pixel.tapad.com 1 redirects footyroom.co
2 ab.dns-finder.com btloader.com
2 jnn-pa.googleapis.com www.youtube.com
2 googleads.g.doubleclick.net 1 redirects www.youtube.com
2 geo.privacymanager.io ats-wrapper.privacymanager.io
2 btloader.com s.nitropay.com
cdn.confiant-integrations.net
2 c.amazon-adsystem.com s.nitropay.com
c.amazon-adsystem.com
2 www.google-analytics.com footyroom.co
www.google-analytics.com
2 cdn.traffmovie.com footyroom.co
cdn.traffmovie.com
2 images.footyroom.com footyroom.co
2 www.googletagmanager.com footyroom.co
www.google-analytics.com
1 csi.gstatic.com pagead2.googlesyndication.com
1 hb.minutemedia-prebid.com srv.scalibur.io
1 direct.adsrvr.org srv.scalibur.io
1 btlr.sharethrough.com srv.scalibur.io
1 stats.g.doubleclick.net www.googletagmanager.com
1 analytics.google.com www.googletagmanager.com
1 secure.cdn.fastclick.net cdn.confiant-integrations.net
1 tags.crwdcntrl.net cdn.confiant-integrations.net
1 cdn.id5-sync.com cdn.confiant-integrations.net
1 a.ad.gt footyroom.co
1 cdn.hadronid.net 1 redirects
1 pixel.rubiconproject.com footyroom.co
1 image6.pubmatic.com footyroom.co
1 lal.p7cloud.net cdn.confiant-integrations.net
1 d3j8vl19c1131u.cloudfront.net cdn.confiant-integrations.net
1 vi.ml314.com cdn.confiant-integrations.net
1 us-u.openx.net cdn.confiant-integrations.net
1 idsync.rlcdn.com cdn.confiant-integrations.net
1 location.p7cloud.net cdn.confiant-integrations.net
1 ua.p7cloud.net cdn.confiant-integrations.net
1 config.aps.amazon-adsystem.com cdn.confiant-integrations.net
1 cdn.api.btloader.com btloader.com
1 cdn.btloader.com cdn.confiant-integrations.net
1 www.gstatic.com www.youtube.com
1 yt3.ggpht.com www.youtube.com
1 call.cleverwebserver.com footyroom.co
1 in.getclicky.com static.getclicky.com
1 www.google.com www.youtube.com
1 static.doubleclick.net www.youtube.com
1 z.cdn.traffmovie.com cdn.traffmovie.com
1 ui.cleverwebserver.com scripts.cleverwebserver.com
1 fonts.googleapis.com ajax.googleapis.com
1 ats-wrapper.privacymanager.io s.nitropay.com
1 floors.nitropay.com s.nitropay.com
1 static.getclicky.com footyroom.co
1 cdnjs.cloudflare.com footyroom.co
1 code.angularjs.org footyroom.co
1 scripts.cleverwebserver.com footyroom.co
0 ssb-global.smartadserver.com Failed srv.scalibur.io
0 ib.adnxs.com Failed cdn.confiant-integrations.net
240 78

This site contains links to these domains. Also see Links.

Domain
www.flashscore.com
nerdytips.com
tribuna.com
youtu.be
www.facebook.com
twitter.com
instagram.com
vk.com
Subject Issuer Validity Valid
footyroom.com
YR2
2026-08-18 -
2026-11-16
3mo crt.sh
nitropay.com
WE1
2026-08-18 -
2026-11-16
3mo crt.sh
*.google.com
WE2
2026-08-10 -
2026-11-02
3mo crt.sh
cleverwebserver.com
WE1
2026-09-05 -
2026-12-04
3mo crt.sh
*.google-analytics.com
WE2
2026-08-10 -
2026-11-02
3mo crt.sh
upload.video.google.com
WE2
2026-08-10 -
2026-11-02
3mo crt.sh
*.g.doubleclick.net
WE2
2026-08-10 -
2026-11-02
3mo crt.sh
spicemob.ca
WR3
2026-09-11 -
2026-12-10
3mo crt.sh
images.footyroom.com
YR1
2026-08-18 -
2026-11-16
3mo crt.sh
cdnjs.cloudflare.com
WE1
2026-09-07 -
2026-12-06
3mo crt.sh
getclicky.com
WE1
2026-08-09 -
2026-11-07
3mo crt.sh
*.nitropay.com
WR3
2026-08-16 -
2026-11-14
3mo crt.sh
*.scalibur.io
Amazon RSA 2048 M04
2026-07-26 -
2027-02-08
7mo crt.sh
*.privacymanager.io
Amazon RSA 2048 M04
2026-04-25 -
2026-11-08
7mo crt.sh
confiant-integrations.net
WE1
2026-08-18 -
2026-11-16
3mo crt.sh
traffmovie.com
YE1
2026-08-31 -
2026-11-29
3mo crt.sh
edgestatic.com
WR2
2026-08-10 -
2026-11-02
3mo crt.sh
*.gstatic.com
WE2
2026-08-10 -
2026-11-02
3mo crt.sh
c.amazon-adsystem.com
Amazon RSA 2048 M04
2025-10-20 -
2026-11-18
1yr crt.sh
*.nit.ro
WR3
2026-08-09 -
2026-11-07
3mo crt.sh
btloader.com
WE1
2026-07-28 -
2026-10-26
3mo crt.sh
*.doubleclick.net
WE2
2026-08-10 -
2026-11-02
3mo crt.sh
*.googleusercontent.com
WE2
2026-08-10 -
2026-11-02
3mo crt.sh
*.p7cloud.net
Amazon RSA 2048 M01
2026-08-13 -
2027-02-26
7mo crt.sh
ad-delivery.net
WE1
2026-08-22 -
2026-11-20
3mo crt.sh
ab.dns-finder.com
WR3
2026-09-09 -
2026-12-08
3mo crt.sh
config.aps.amazon-adsystem.com
Amazon RSA 2048 M04
2025-11-23 -
2026-12-22
1yr crt.sh
gw.geoedge.be
Amazon RSA 2048 M04
2026-05-11 -
2026-11-24
7mo crt.sh
*.rlcdn.com
Sectigo Public Server Authentication CA DV R36
2026-02-05 -
2027-03-05
1yr crt.sh
*.openx.net
RapidSSL TLS RSA CA G1
2026-07-18 -
2027-02-01
7mo crt.sh
vi.ml314.com
WR3
2026-08-26 -
2026-11-24
3mo crt.sh
*.cloudfront.net
Amazon RSA 2048 M04
2026-08-25 -
2027-03-10
7mo crt.sh
*.pubmatic.com
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2026-02-18 -
2027-03-19
1yr crt.sh
*.rubiconproject.com
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2026-08-31 -
2027-03-17
7mo crt.sh
id5-sync.com
WE1
2026-09-09 -
2026-12-08
3mo crt.sh
*.crwdcntrl.net
Amazon RSA 2048 M04
2026-07-10 -
2027-01-23
7mo crt.sh
secure.cdn.fastclick.net
YR2
2026-07-27 -
2026-10-25
3mo crt.sh
jsdelivr.net
GlobalSign Atlas R3 DV TLS CA 2026 Q2
2026-05-20 -
2026-12-05
7mo crt.sh
id.hadron.ad.gt
WE1
2026-08-29 -
2026-11-27
3mo crt.sh
*.adsrvr.org
GlobalSign GCC R3 DV TLS CA 2020
2026-03-04 -
2027-04-02
1yr crt.sh
eu-1-id5-sync.com
YR1
2026-09-01 -
2026-11-30
3mo crt.sh
*.sharethrough.com
DigiCert Global G3 TLS ECC SHA384 2020 CA1
2026-08-06 -
2027-02-19
7mo crt.sh
*.media.net
Sectigo Public Server Authentication CA DV E36
2026-04-16 -
2026-10-31
7mo crt.sh
*.targeting.unrulymedia.com
Sectigo Public Server Authentication CA DV R36
2026-04-14 -
2026-10-29
7mo crt.sh
*.minutemedia-prebid.com
WR3
2026-08-03 -
2026-11-01
3mo crt.sh

This page contains 20 frames:

Primary Page: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Frame ID: 0A3615CC6CFBF1C23A7B2BB1522B762E
Requests: 149 HTTP requests in this frame

Frame: https://www.youtube.com/embed/ch_4efPW8xc?rel=0
Frame ID: 6906A5180F7FEBF7CE2E39CF8F3DBEDD
Requests: 17 HTTP requests in this frame

Frame: blob://https://footyroom.co/f9962497-5425-4f42-889f-0acd9e99c7b5
Frame ID: D46FCFCD0D4C007FAF4BE3B9ED9F2CA0
Requests: 1 HTTP requests in this frame

Frame: https://cdn.btloader.com/cchecker.html?upapi=true
Frame ID: FD0EF515AF15DCCDC040EA3E2A47B4A3
Requests: 1 HTTP requests in this frame

Frame: https://btloader.com/trustedIframe.html?o=6278260873756672&upapi=true
Frame ID: B49C8AD0EAF0B805B9E4F053CC1A9005
Requests: 1 HTTP requests in this frame

Frame: https://srv.scalibur.io/adserver/adunit?id=56&width=970&height=90&url=https%3A%2F%2Ffootyroom.co%2Fmatches%2F80034717%2Fmanchester-united-vs-sabah-fk%2Freview&sids=%7B%7D&schain=1.0%2C1!nitropay.com%2C1728%2C1%2C%2C%2C&containerId=Match%20Highlights-isolated&isDebug=0&cb=1789351873336_kzlsm4&us_privacy=1---&keyValues=%7B%22gamAdUnitId%22%3A%22%2F308365556%2C22913055933%2Fnitro-banner%2Fnitro-banner-2321%22%2C%22ttdPubId%22%3A%221728%22%2C%22siteId%22%3A%222321%22%2C%22nitro_gpid%22%3A%22Match%20Highlights%22%7D
Frame ID: 9E78AA3ACA058822248870D328C40A5B
Requests: 9 HTTP requests in this frame

Frame: https://srv.scalibur.io/adserver/adunit?id=56&width=300&height=169&url=https%3A%2F%2Ffootyroom.co%2Fmatches%2F80034717%2Fmanchester-united-vs-sabah-fk%2Freview&sids=%7B%7D&schain=1.0%2C1!nitropay.com%2C1728%2C1%2C%2C%2C&containerId=Nitro%20Desktop%20Video%20Ad-isolated&isDebug=0&cb=1789351873339_1cdfuw&us_privacy=1---&keyValues=%7B%22gamAdUnitId%22%3A%22%2F308365556%2C22913055933%2Fnitro-banner%2Fnitro-banner-2321%22%2C%22ttdPubId%22%3A%221728%22%2C%22siteId%22%3A%222321%22%2C%22nitro_gpid%22%3A%22Nitro%20Desktop%20Video%20Ad%22%7D
Frame ID: 14B4C4681C19D751FC80916F7BAB23C4
Requests: 9 HTTP requests in this frame

Frame: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Frame ID: 22B1858B2612E9D8E7D9096D20A053AC
Requests: 17 HTTP requests in this frame

Frame: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Frame ID: A4C8C22889E889DC9C291F833DC3E51B
Requests: 19 HTTP requests in this frame

Frame: https://silo60.p7cloud.net/if.html?gdpr=false&gdprConsent=false&tpd=true&md=false
Frame ID: 2244AAEDC8A800DE69CC91EABFFC255F
Requests: 5 HTTP requests in this frame

Frame: https://rumcdn.geoedge.be/3c5f792e-2099-4b89-b2fa-171ced5152e0/grumi.js
Frame ID: F45083F619726F9D87D875A0804D93D7
Requests: 1 HTTP requests in this frame

Frame: https://rumcdn.geoedge.be/3c5f792e-2099-4b89-b2fa-171ced5152e0/grumi.js
Frame ID: 7B7188A28B8F53DA123A183AD251BA6A
Requests: 1 HTTP requests in this frame

Frame: https://idsync.rlcdn.com/713229.gif?partner_uid=silo60:ae025c43-b265-4e9c-856f-17be8af12f8f
Frame ID: A2A923B536817DD3066A671D88ECDDE5
Requests: 1 HTTP requests in this frame

Frame: https://us-u.openx.net/w/1.0/cm?id=7f21a24f-7b81-4961-8928-1f1339490a93&gdpr=0&gdpr_consent=&us_privacy=&gpp=&gpp_sid=-1&r=https%3A%2F%2Fsync.p7cloud.net%2Fp.png%3Fopenx_id%3D{OPENX_ID}%26arcid%3Dsilo60%253Aae025c43-b265-4e9c-856f-17be8af12f8f
Frame ID: A25CF3B86AB1B4272479E6023F6B6853
Requests: 1 HTTP requests in this frame

Frame: https://imasdk.googleapis.com/js/core/bridge3.789.0_en.html
Frame ID: 6E467636342FCEE15E5F545EC69E1BB4
Requests: 1 HTTP requests in this frame

Frame: https://pagead2.googlesyndication.com/omsdk/releases/live/omweb-v1.js
Frame ID: FEB56CD640E496C6F0BAC5B21AF659B3
Requests: 1 HTTP requests in this frame

Frame: https://imasdk.googleapis.com/js/core/bridge3.789.0_en.html
Frame ID: 0AB74FE5F1315A4AD93FA11DBF0FBEC2
Requests: 1 HTTP requests in this frame

Frame: https://pagead2.googlesyndication.com/omsdk/releases/live/omweb-v1.js
Frame ID: 2E937CD9AA6A8F6929ACD7ECEE0E8AB0
Requests: 1 HTTP requests in this frame

Frame: https://srv.scalibur.io/adserver/sync?type=iframe&gdpr=1&gdpr_consent=&us_privacy=1---&gpp=&gpp_sid=
Frame ID: 977129C6D97C4CE5E94A6E92F50323D6
Requests: 1 HTTP requests in this frame

Frame: https://srv.scalibur.io/adserver/sync?type=iframe&gdpr=1&gdpr_consent=&us_privacy=1---&gpp=&gpp_sid=
Frame ID: 5B9764C31D97C0805CAA26434A406566
Requests: 1 HTTP requests in this frame

Screenshot Go Pro

Only in urlscan Pro

Use the Visual Search feature to find pages with visually similar screenshots.
Click for more information
Free trials of urlscan Pro are available.

Page Title

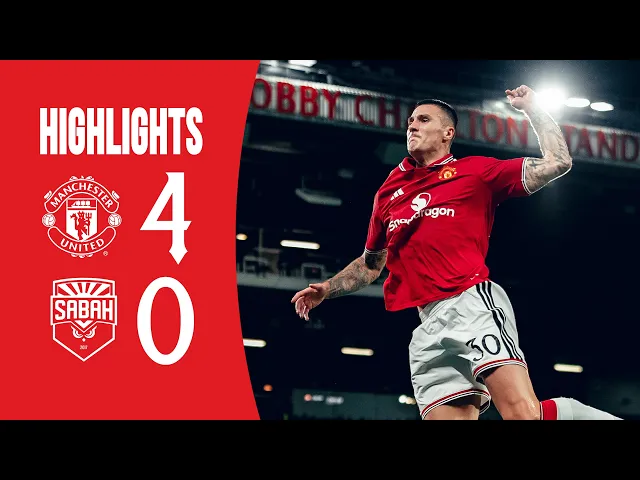
Manchester United 4-0 Sabah FK Highlights, Goals & Key Moments (10 Sep 2026) | Champions League - FootyRoom

Detected technologies

(Video players)
Overall confidence: 100%
Detected patterns
  • \.youtube\.com/

(JavaScript frameworks)
Overall confidence: 100%
Detected patterns
  • /([\d.]+(?:-?rc[.\d]*)*)/angular(?:\.min)?\.js
  • (?!angular\.io)\bangular.{0,32}\.js

(JavaScript frameworks)
Overall confidence: 100%
Detected patterns
  • socket\.io.*\.js

(Advertising)
Overall confidence: 100%
Detected patterns
  • \.amazon-adsystem\.com

(Advertising)
Overall confidence: 100%
Detected patterns

(CDN)
Overall confidence: 100%
Detected patterns
  • cdnjs\.cloudflare\.com

(Analytics)
Overall confidence: 100%
Detected patterns
  • static\.getclicky\.com

(Security)
Overall confidence: 100%
Detected patterns

(Advertising)
Overall confidence: 100%
Detected patterns
  • 2mdn\.net

(Advertising)
Overall confidence: 100%
Detected patterns
  • \.doubleclick\.net

(Cookie compliance)
Overall confidence: 100%
Detected patterns
  • fundingchoicesmessages\.google\.com

(Advertising)
Overall confidence: 100%
Detected patterns
  • googlesyndication\.com/
  • 2mdn\.net

(Analytics)
Overall confidence: 100%
Detected patterns
  • google-analytics\.com/(?:ga|urchin|analytics)\.js
  • googletagmanager\.com/gtag/js

(Font scripts)
Overall confidence: 100%
Detected patterns
  • googleapis\.com/.+webfont

(CDN)
Overall confidence: 100%
Detected patterns
  • ajax\.googleapis\.com/ajax/libs/

(Advertising)
Overall confidence: 100%
Detected patterns
  • securepubads\.g\.doubleclick.net/tag/js/gpt\.js

(Tag managers)
Overall confidence: 100%
Detected patterns
  • <!-- (?:End )?Google Tag Manager -->
  • googletagmanager\.com/gtm\.js
  • \.googletagmanager\.com/

(Advertising)
Overall confidence: 100%
Detected patterns
  • ^https://(?:cdn\.)?id5-sync\.com/

(JavaScript libraries)
Overall confidence: 100%
Detected patterns
  • jquery
  • /(\d+\.\d+\.\d+)/jquery(?!\.popupoverlay\.js|(?:\.[\w-]*)*fancybox)[/.-][^u]

(CDN)
Overall confidence: 100%
Detected patterns
  • cdn\.jsdelivr\.net

(Advertising)
Overall confidence: 100%
Detected patterns
  • \.media\.net/

(Advertising)
Overall confidence: 100%
Detected patterns
  • https?://[^/]*\.openx\.net

(Advertising)
Overall confidence: 100%
Detected patterns
  • https?://[^/]*\.pubmatic\.com

(Advertising)
Overall confidence: 100%
Detected patterns
  • https?://[^/]*\.rubiconproject\.com

(Advertising)
Overall confidence: 100%
Detected patterns
  • \.sharethrough\.com/

(Advertising)
Overall confidence: 100%
Detected patterns
  • \.adsrvr\.org/

Page Statistics

240
Requests

98 %
HTTPS

45 %
IPv6

50
Domains

78
Subdomains

71
IPs

8
Countries

5221 kB
Transfer

19303 kB
Size

34
Cookies

Redirected requests

There were HTTP redirect chains for the following requests:

Request Chain 90
  • https://googleads.g.doubleclick.net/pagead/id HTTP 302
  • https://googleads.g.doubleclick.net/pagead/id?slf_rd=1
Request Chain 143
  • https://pixel.tapad.com/idsync/ex/receive?partner_id=3416&partner_device_id=silo60:ae025c43-b265-4e9c-856f-17be8af12f8f HTTP 302
  • https://pixel.tapad.com/idsync/ex/receive/check?partner_id=3416&partner_device_id=silo60:ae025c43-b265-4e9c-856f-17be8af12f8f
Request Chain 146
  • https://cdn.hadronid.net/hadron.js?url=https%3A%2F%2Ffootyroom.co%2Fmatches%2F80034717%2Fmanchester-united-vs-sabah-fk%2Freview&ref=&_it=amazon&partner_id=720 HTTP 301
  • https://a.ad.gt/api/v1/u/matches/720?_it=nitro

240 HTTP transactions Go Pro

Only in urlscan Pro

Inspect WebSocket connections, examine POST data effortlessly, and track overlap counts in real time. Features live search and filtering across all HTTP output, complete with full response metadata for deep analysis.
Click for more information
Free trials of urlscan Pro are available.

0 data transactions

Method
Protocol
Status Resource
Path
Size
x-fer
Time
Latency
Type
MIME-Type
IP
Location
GET
H2
200
Primary Request review Show response
footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/
186 KB
55 KB
1336ms
1295ms
Document
text/html
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx / PHP/7.3.7-1+0~20190710.40+debian9~1.gbp032aec
Resource Hash
6c0a003ae339daa9b04d224ffe58f4d0493097502cfb0428f90f33b3a2a3f144
Security Headers
Name Value
Strict-Transport-Security max-age=2592000; includeSubDomains
X-Frame-Options sameorigin

Request headers

Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

cache-control
no-cache, private
content-encoding
gzip
content-type
text/html; charset=UTF-8
date
Mon, 14 Sep 2026 02:11:11 GMT
server
nginx
strict-transport-security
max-age=2592000; includeSubDomains
vary
Accept-Encoding
x-frame-options
sameorigin
x-powered-by
PHP/7.3.7-1+0~20190710.40+debian9~1.gbp032aec
GET
H3
200
ads-2321.js Show response
s.nitropay.com/
696 KB
233 KB
56ms
28ms
Script
text/javascript
104.18.3.78
Cloudflare
General
Full URL
https://s.nitropay.com/ads-2321.js
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.18.3.78 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
c89168d63346530e40becb11bee9961f8f4ac204aa123d5ad6bc48e608ecc77d
Security Headers
Name Value
Strict-Transport-Security max-age=2592000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
access-control-expose-headers
Content-Type
x-goog-meta-goog-reserved-file-mtime
1789157733
x-goog-hash
crc32c=YCHbhg==, md5=5LNbhhkvRMsMjZkirzdK4g==
cf-cache-status
HIT
etag
W/"e4b35b86192f44cb0c8d9922af374ae2:1789299262000:NL"
age
52584
content-encoding
gzip
x-goog-stored-content-encoding
identity
expires
Mon, 13 Sep 2027 11:34:47 GMT
alt-svc
h3=":443"; ma=86400
x-goog-stored-content-length
707060
server-timing
cfExtPri
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
text/javascript
last-modified
Sun, 13 Sep 2026 11:34:22 GMT
priority
u=3,i=?0
x-guploader-uploadid
AJjja9YcsedBNXxK5Gr0QC9PjhdO0An39IUrz8rTtyxJnYZ7Fu9ITUAueWEmfH2HuFzHi22N
strict-transport-security
max-age=2592000; includeSubDomains
cache-control
private, max-age=600
x-goog-storage-class
MULTI_REGIONAL
cf-ray
a3abdc10788efba3-AMS
access-control-allow-origin
*
x-goog-generation
1789158258952298
server
cloudflare
GET
H2
200
pub-7050889928379236 Show response
fundingchoicesmessages.google.com/i/
223 KB
71 KB
153ms
62ms
Script
application/javascript
2a00:1450:4001:c15::66
Google LLC
General
Full URL
https://fundingchoicesmessages.google.com/i/pub-7050889928379236?ers=1
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a00:1450:4001:c15::66 Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
1f925ed18b954f626b23e794fee28b231aea291baf15dcd412c1e13331335581
Security Headers
Name Value
Content-Security-Policy script-src 'report-sample' 'nonce-lram471aVPXOnmnxegDaxg' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/ContributorServingWebSwitchboardHttp/cspreport;worker-src 'self', script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/ContributorServingWebSwitchboardHttp/cspreport/allowlist, require-trusted-types-for 'script';report-uri /_/ContributorServingWebSwitchboardHttp/cspreport
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-content-type-options
nosniff
expires
Mon, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
application/javascript; charset=utf-8
x-frame-options
SAMEORIGIN
reporting-endpoints
default="/_/ContributorServingWebSwitchboardHttp/web-reports?context=eJzjytHikmLw0ZBiOHnrNtNFIG69eY51OhCXLDrP2gbEXUA8B4gNFS6xOgPxh_rLrD-AuEjiCmsLEH-qusEqUn2D9VuxLxtHiS8by1t_toXTAtlWArGIQRCbDBCnHQxnywNiIW6OA-vnXmUTOPFolreSRlJ-YXxyfl5JUWZSaUl-UVpyWmpxalFZalG8kYGRmYGlgaWeoWF8gQEAuhU_lw"
content-security-policy
script-src 'report-sample' 'nonce-lram471aVPXOnmnxegDaxg' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/ContributorServingWebSwitchboardHttp/cspreport;worker-src 'self', script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/ContributorServingWebSwitchboardHttp/cspreport/allowlist, require-trusted-types-for 'script';report-uri /_/ContributorServingWebSwitchboardHttp/cspreport
cache-control
no-cache, no-store, max-age=0, must-revalidate
timing-allow-origin
*
cross-origin-opener-policy
same-origin
pragma
no-cache
accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
cross-origin-resource-policy
cross-origin
permissions-policy
ch-ua-arch=*, ch-ua-bitness=*, ch-ua-full-version=*, ch-ua-full-version-list=*, ch-ua-model=*, ch-ua-wow64=*, ch-ua-form-factors=*, ch-ua-platform=*, ch-ua-platform-version=*
x-xss-protection
0
server
ESF
GET
H2
200
746d84c846e7a9d594919df4eab520e7.js Show response
scripts.cleverwebserver.com/
99 KB
29 KB
78ms
34ms
Script
application/javascript
2606:4700:4405::6812:21f7
Cloudflare
General
Full URL
https://scripts.cleverwebserver.com/746d84c846e7a9d594919df4eab520e7.js
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2606:4700:4405::6812:21f7 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
cf1fff001247fbdb3136382840a430c7c3a056d032347c0fcd7bb2d8731ff7fa

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
public, max-age=1800
content-encoding
br
cf-cache-status
HIT
x-amz-version-id
N2tvxTshbe4Hvbd6F_HNbf_nO0UqjQ_R
etag
W/"de1ab8def5ca03c55690afa81f7abf13"
x-amz-request-id
8ES7SNFXXT69XM3Q
expires
Mon, 14 Sep 2026 02:41:12 GMT
cf-ray
a3abdc126fce285a-AMS
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
application/javascript
last-modified
Thu, 03 Sep 2026 14:09:54 GMT
server
cloudflare
x-amz-id-2
HoveqiacJyCYjceYDyg5n7PWRCZWxvAyPERRoCP8pLkC0Xcn8Bld3ydHJWqHYeWX2RgjSEx6ucg=
GET
H2
200
gtm.js Show response
www.googletagmanager.com/
324 KB
115 KB
159ms
64ms
Script
application/javascript
2a00:1450:4001:c15::61
Google LLC
General
Full URL
https://www.googletagmanager.com/gtm.js?id=GTM-TT54HBD
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a00:1450:4001:c15::61 Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
Google Tag Manager /
Resource Hash
1c15b7b8a29622472026b9de49587091037c06d04f00bca8c5cf98bfd4fc7c7e
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
zstd
expires
Mon, 14 Sep 2026 02:11:12 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
last-modified
Mon, 14 Sep 2026 00:00:00 GMT
access-control-allow-headers
Cache-Control
strict-transport-security
max-age=31536000; includeSubDomains
cache-control
private, max-age=900
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
access-control-allow-origin
*
content-length
117331
x-xss-protection
0
server
Google Tag Manager
GET
H2
200
webfont.js Show response
ajax.googleapis.com/ajax/libs/webfont/1.6.26/
13 KB
6 KB
132ms
39ms
Script
text/javascript
2a00:1450:4001:c0f::5f
Google LLC
General
Full URL
https://ajax.googleapis.com/ajax/libs/webfont/1.6.26/webfont.js
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a00:1450:4001:c0f::5f Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
81016ac6be850b72df5d4faa0c3cec8e2c1b0ba0045712144a6766adfad40bee
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
age
96799
report-to
{"group":"hosted-libraries-pushers","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/hosted-libraries-pushers"}]}
x-content-type-options
nosniff
expires
Sun, 12 Sep 2027 23:17:53 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sat, 12 Sep 2026 23:17:53 GMT
last-modified
Tue, 03 Mar 2020 19:15:00 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
cache-control
public, max-age=31536000, stale-while-revalidate=2592000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="hosted-libraries-pushers"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/hosted-libraries-pushers
accept-ranges
bytes
access-control-allow-origin
*
content-length
5437
x-xss-protection
0
server
sffe
GET
H3
200
gpt.js Show response
securepubads.g.doubleclick.net/tag/js/
125 KB
38 KB
107ms
58ms
Script
text/javascript
142.251.127.156
Google LLC
General
Full URL
https://securepubads.g.doubleclick.net/tag/js/gpt.js
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.127.156 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfrai-in-f156.1e100.net
Software
cafe /
Resource Hash
fb5290615c75705d27dded2a331aac90e6c5eabba48941bbd78b52c3af158975
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://footyroom.co
sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
etag
128 / 20710 / 122880985 / config-hash: 17945051965659213301
x-content-type-options
nosniff
expires
Mon, 14 Sep 2026 02:11:12 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-disposition
attachment; filename="f.txt"
cache-control
private, max-age=900, stale-while-revalidate=3600
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
content-length
38384
x-xss-protection
0
server
cafe
GET
H2
200
jquery.min.js Show response
ajax.googleapis.com/ajax/libs/jquery/1.10.2/
91 KB
32 KB
133ms
41ms
Script
text/javascript
2a00:1450:4001:c0f::5f
Google LLC
General
Full URL
https://ajax.googleapis.com/ajax/libs/jquery/1.10.2/jquery.min.js
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a00:1450:4001:c0f::5f Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
89a15e9c40bc6b14809f236ee8cd3ed1ea42393c1f6ca55c7855cd779b3f922e
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
age
103026
report-to
{"group":"hosted-libraries-pushers","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/hosted-libraries-pushers"}]}
x-content-type-options
nosniff
expires
Sun, 12 Sep 2027 21:34:06 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sat, 12 Sep 2026 21:34:06 GMT
last-modified
Tue, 03 Mar 2020 19:15:00 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
cache-control
public, max-age=31536000, stale-while-revalidate=2592000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="hosted-libraries-pushers"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/hosted-libraries-pushers
accept-ranges
bytes
access-control-allow-origin
*
content-length
32954
x-xss-protection
0
server
sffe
GET
H2
200
angular.min.js Show response
ajax.googleapis.com/ajax/libs/angularjs/1.5.8/
156 KB
55 KB
180ms
87ms
Script
text/javascript
2a00:1450:4001:c0f::5f
Google LLC
General
Full URL
https://ajax.googleapis.com/ajax/libs/angularjs/1.5.8/angular.min.js
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a00:1450:4001:c0f::5f Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
e92af41ea36051ffe9f3c83abec97cec2ac09cdaa2396863958e8b4bc8de5870
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
age
212731
report-to
{"group":"hosted-libraries-pushers","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/hosted-libraries-pushers"}]}
x-content-type-options
nosniff
expires
Sat, 11 Sep 2027 15:05:41 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 11 Sep 2026 15:05:41 GMT
last-modified
Tue, 03 Mar 2020 19:15:00 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
cache-control
public, max-age=31536000, stale-while-revalidate=2592000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="hosted-libraries-pushers"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/hosted-libraries-pushers
accept-ranges
bytes
access-control-allow-origin
*
content-length
56572
x-xss-protection
0
server
sffe
GET
H2
200
angular-sanitize.min.js Show response
code.angularjs.org/1.5.8/
6 KB
4 KB
74ms
15ms
Script
application/javascript
151.101.1.195
Fastly
General
Full URL
https://code.angularjs.org/1.5.8/angular-sanitize.min.js
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.1.195 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
Google Frontend /
Resource Hash
aa798163f47e11eda70c68669b4e75f7f694f429fceba154b606263a583b57b3
Security Headers
Name Value
Strict-Transport-Security max-age=31556926

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-orig-accept-language
fr-FR,fr;q=0.9,pt;q=0.8,en-US;q=0.7,en;q=0.6,es;q=0.5
alt-svc
h3=":443";ma=86400,h3-29=":443";ma=86400,h3-27=":443";ma=86400
x-country-code
LU
x-cache
HIT
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
application/javascript; charset=utf-8
vary
cookie,need-authorization, x-fh-requested-host, accept-encoding
x-cache-hits
0
x-cloud-trace-context
97056646544fc5b20f3b6e6a73790f6b
x-served-by
cache-rtm-ehrd2290049-RTM
strict-transport-security
max-age=31556926
cache-control
public, max-age=600, s-maxage=43200
x-timer
S1789351872.113461,VS0,VE1
accept-ranges
bytes
content-length
3174
function-execution-id
1r5mjxzbmh96
server
Google Frontend
GET
H2
200
runtime.975dcd22e3dc620cb1fe.js Show response
cdn.footyroom.co/js/dist/
2 KB
1 KB
99ms
50ms
Script
application/javascript
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://cdn.footyroom.co/js/dist/runtime.975dcd22e3dc620cb1fe.js
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
1d9ef22e5168f1b0cdafc63048b210705b4edd54378c874fdc58843110de375e

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000, public
content-encoding
gzip
etag
W/"6a6d871d-8e0"
pragma
public
expires
Wed, 14 Oct 2026 02:11:12 GMT
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
application/javascript
last-modified
Sat, 01 Aug 2026 05:41:49 GMT
server
nginx
vary
Accept-Encoding
GET
H2
200
vendors.970b.63925cd0805ceba21817.js Show response
cdn.footyroom.co/js/dist/
2 KB
1 KB
97ms
48ms
Script
application/javascript
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://cdn.footyroom.co/js/dist/vendors.970b.63925cd0805ceba21817.js
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
563e1f9a52535fbc9800a8a1047cb55e4a913a751da2c6a1ee9b4e9ed9ef4302

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000, public
content-encoding
gzip
etag
W/"6a6d871d-8fe"
pragma
public
expires
Wed, 14 Oct 2026 02:11:12 GMT
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
application/javascript
last-modified
Sat, 01 Aug 2026 05:41:49 GMT
server
nginx
vary
Accept-Encoding
GET
H2
200
vendors.c5ee.98860b2ce2be8febc4ac.js Show response
cdn.footyroom.co/js/dist/
1 KB
825 B
100ms
52ms
Script
application/javascript
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://cdn.footyroom.co/js/dist/vendors.c5ee.98860b2ce2be8febc4ac.js
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
dd4505c10dcc23ccb77ebee92ca3fbe0a8e57a352fcda6c2a7a780cca27b9370

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000, public
content-encoding
gzip
etag
W/"6a6d871d-400"
pragma
public
expires
Wed, 14 Oct 2026 02:11:12 GMT
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
application/javascript
last-modified
Sat, 01 Aug 2026 05:41:49 GMT
server
nginx
vary
Accept-Encoding
GET
H2
200
vendors.148c.573b62bb1f774a0a5539.js Show response
cdn.footyroom.co/js/dist/
44 KB
15 KB
98ms
49ms
Script
application/javascript
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://cdn.footyroom.co/js/dist/vendors.148c.573b62bb1f774a0a5539.js
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
5d055cefe58e49c6c6c4b14972a9c9746edba9ebbe4dc3f02d1ddd96a7555a7a

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000, public
content-encoding
gzip
etag
W/"6a6d871d-b161"
pragma
public
expires
Wed, 14 Oct 2026 02:11:12 GMT
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
application/javascript
last-modified
Sat, 01 Aug 2026 05:41:49 GMT
server
nginx
vary
Accept-Encoding
GET
H2
200
decc.7a7824742eff4529d1d3.js Show response
cdn.footyroom.co/js/dist/
5 KB
2 KB
90ms
42ms
Script
application/javascript
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://cdn.footyroom.co/js/dist/decc.7a7824742eff4529d1d3.js
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
c37bd01b17d46c77c441509b68bde27e8cd6d8d8f767d67a59708649e35b56fa

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000, public
content-encoding
gzip
etag
W/"6a6d871d-13ac"
pragma
public
expires
Wed, 14 Oct 2026 02:11:12 GMT
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
application/javascript
last-modified
Sat, 01 Aug 2026 05:41:49 GMT
server
nginx
vary
Accept-Encoding
GET
H2
200
ef19.0790a598482b009df7f3.js Show response
cdn.footyroom.co/js/dist/
1 KB
851 B
97ms
48ms
Script
application/javascript
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://cdn.footyroom.co/js/dist/ef19.0790a598482b009df7f3.js
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
1cb3f65a88a78e2ec2bbf0aca1a9a084cbc2ad976ca4aa77f5f55a16ba6e55ad

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000, public
content-encoding
gzip
etag
W/"6a6d871d-4e3"
pragma
public
expires
Wed, 14 Oct 2026 02:11:12 GMT
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
application/javascript
last-modified
Sat, 01 Aug 2026 05:41:49 GMT
server
nginx
vary
Accept-Encoding
GET
H2
200
1ae7.48e5b3e0041d070e68e8.js Show response
cdn.footyroom.co/js/dist/
530 B
539 B
97ms
49ms
Script
application/javascript
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://cdn.footyroom.co/js/dist/1ae7.48e5b3e0041d070e68e8.js
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
f6cf1bb42463700483b7472989d3aae6d0005ae0d7548290e4a920bb0216c0e2

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000, public
content-encoding
gzip
etag
W/"6a6d871d-212"
pragma
public
expires
Wed, 14 Oct 2026 02:11:12 GMT
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
application/javascript
last-modified
Sat, 01 Aug 2026 05:41:49 GMT
server
nginx
vary
Accept-Encoding
GET
H2
200
main.99eb6ce37462b63a33e1.js Show response
cdn.footyroom.co/js/dist/
24 KB
9 KB
97ms
49ms
Script
application/javascript
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://cdn.footyroom.co/js/dist/main.99eb6ce37462b63a33e1.js
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
6333d5adf5474f221fea5509b5c056acf0b11f959961cbb3d6a95fddcd9640e0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000, public
content-encoding
gzip
etag
W/"6a6d871d-5f1c"
pragma
public
expires
Wed, 14 Oct 2026 02:11:12 GMT
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
application/javascript
last-modified
Sat, 01 Aug 2026 05:41:49 GMT
server
nginx
vary
Accept-Encoding
GET
H2
200
vendors.1090.31f9ac0514e535ec0ba7.js Show response
cdn.footyroom.co/js/dist/
3 KB
2 KB
91ms
43ms
Script
application/javascript
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://cdn.footyroom.co/js/dist/vendors.1090.31f9ac0514e535ec0ba7.js
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
ccc0edbb4bcec0278d2fc9fb02d8edc440152a411ad9b7de97175e5cfd917d7f

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000, public
content-encoding
gzip
etag
W/"6a6d871d-c51"
pragma
public
expires
Wed, 14 Oct 2026 02:11:12 GMT
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
application/javascript
last-modified
Sat, 01 Aug 2026 05:41:49 GMT
server
nginx
vary
Accept-Encoding
GET
H2
200
91fe.dd95efc691d4c1b42316.js Show response
cdn.footyroom.co/js/dist/
518 B
571 B
97ms
50ms
Script
application/javascript
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://cdn.footyroom.co/js/dist/91fe.dd95efc691d4c1b42316.js
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
0208b97373fa96b5919799803d8baeff65f5ac1e59b51efb7662ac66362f4c08

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000, public
content-encoding
gzip
etag
W/"6a6d871d-206"
pragma
public
expires
Wed, 14 Oct 2026 02:11:12 GMT
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
application/javascript
last-modified
Sat, 01 Aug 2026 05:41:49 GMT
server
nginx
vary
Accept-Encoding
GET
H2
200
14aa.716912755037dcf5abf6.js Show response
cdn.footyroom.co/js/dist/
15 KB
5 KB
96ms
48ms
Script
application/javascript
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://cdn.footyroom.co/js/dist/14aa.716912755037dcf5abf6.js
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
b9d6ce05e3e9f7572d7c627ff63065d55a873610b1fe46b6c96a386707d4c788

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000, public
content-encoding
gzip
etag
W/"6a6d871d-3ae2"
pragma
public
expires
Wed, 14 Oct 2026 02:11:12 GMT
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
application/javascript
last-modified
Sat, 01 Aug 2026 05:41:49 GMT
server
nginx
vary
Accept-Encoding
GET
H2
200
028d.ebf3fe8b67249db14806.js Show response
cdn.footyroom.co/js/dist/
2 KB
1 KB
90ms
43ms
Script
application/javascript
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://cdn.footyroom.co/js/dist/028d.ebf3fe8b67249db14806.js
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
e8e0579f3cea977b499274b637aac97822de6f09f81f244bb2022c7a015289b4

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000, public
content-encoding
gzip
etag
W/"6a6d871d-7a1"
pragma
public
expires
Wed, 14 Oct 2026 02:11:12 GMT
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
application/javascript
last-modified
Sat, 01 Aug 2026 05:41:49 GMT
server
nginx
vary
Accept-Encoding
GET
H2
200
review.f3471f03ef244e075eef.js Show response
cdn.footyroom.co/js/dist/
4 KB
2 KB
90ms
43ms
Script
application/javascript
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://cdn.footyroom.co/js/dist/review.f3471f03ef244e075eef.js
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
179110bbab4e2b0a8a5407d05e02c57cc1d98fcc745c3633e4ea763b0eda664b

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000, public
content-encoding
gzip
etag
W/"6a6d871d-1010"
pragma
public
expires
Wed, 14 Oct 2026 02:11:12 GMT
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
application/javascript
last-modified
Sat, 01 Aug 2026 05:41:49 GMT
server
nginx
vary
Accept-Encoding
GET
H2
200
c50d.8aca0796798ede721465.js Show response
cdn.footyroom.co/js/dist/
6 KB
2 KB
95ms
48ms
Script
application/javascript
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://cdn.footyroom.co/js/dist/c50d.8aca0796798ede721465.js
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
be1b45c1607894fd608f8a3f2075d68b278b4f0ac0c1a6df123e1582fde43adf

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000, public
content-encoding
gzip
etag
W/"6a6d871d-1673"
pragma
public
expires
Wed, 14 Oct 2026 02:11:12 GMT
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
application/javascript
last-modified
Sat, 01 Aug 2026 05:41:49 GMT
server
nginx
vary
Accept-Encoding
GET
H2
200
talkroom.bc3f4104fe94a51393c8.js Show response
cdn.footyroom.co/js/dist/
9 KB
4 KB
95ms
47ms
Script
application/javascript
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://cdn.footyroom.co/js/dist/talkroom.bc3f4104fe94a51393c8.js
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
8c15e64745dad33d026db42c28b620ee9f4f16d7dbffb3f24649fc69bb64205a

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000, public
content-encoding
gzip
etag
W/"6a6d871d-2255"
pragma
public
expires
Wed, 14 Oct 2026 02:11:12 GMT
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
application/javascript
last-modified
Sat, 01 Aug 2026 05:41:49 GMT
server
nginx
vary
Accept-Encoding
GET
H3
200
socket.io.slim.js Show response
cdnjs.cloudflare.com/ajax/libs/socket.io/2.2.0/
52 KB
14 KB
43ms
26ms
Script
application/javascript
104.17.25.14
Cloudflare
General
Full URL
https://cdnjs.cloudflare.com/ajax/libs/socket.io/2.2.0/socket.io.slim.js
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.17.25.14 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
46d313ada07980694b111d0590a05c6970a6642402c64292fdd5e6ecc484a046
Security Headers
Name Value
Strict-Transport-Security max-age=15780000
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cf-cdnjs-via
cfworker/r2
content-encoding
br
cf-cache-status
BYPASS
age
5238565
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=f%2FOr%2BLPZmBxZ5T%2Fr2JtvoxdCCRkCsY3jgpCAD2inuL8CODQ%2FbDXpvWAJUrW3LDxFiK76XD2FxJhVWYNN7pR9qPRI2OUlk1SRxg5feRZ7SuUQKLJewUWt5%2FJ3jNJigzuHLvv6V5Sr"}]}
x-content-type-options
nosniff
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
x-cdnjs-cache
HIT
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
application/javascript; charset=utf-8
last-modified
Mon, 04 May 2020 16:16:21 GMT
vary
Accept-Encoding
priority
u=1,i=?0
strict-transport-security
max-age=15780000
cache-control
no-transform, public, s-maxage=30672000, max-age=30672000, immutable
timing-allow-origin
*
nel
{"report_to":"cf-nel","success_fraction":0.01,"max_age":604800}
cross-origin-resource-policy
cross-origin
cf-ray
a3abdc107aca37c0-AMS
access-control-allow-origin
*
content-length
13920
server
cloudflare
GET
H2
200
main.89f0a2fe7e05d3174bba.css
cdn.footyroom.co/css/dist/
139 KB
34 KB
63ms
17ms
Stylesheet
text/css
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://cdn.footyroom.co/css/dist/main.89f0a2fe7e05d3174bba.css
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
899930caa73eef59d0670826b7dd81ad480a8bb66c6074ff6c79f23928d0e6c6

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000, public
content-encoding
gzip
etag
W/"6a6d871d-22d10"
pragma
public
expires
Wed, 14 Oct 2026 02:11:12 GMT
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
text/css
last-modified
Sat, 01 Aug 2026 05:41:49 GMT
server
nginx
vary
Accept-Encoding
GET
H3
200
js Show response
static.getclicky.com/
12 KB
5 KB
51ms
24ms
Script
text/javascript
104.16.225.240
Cloudflare
General
Full URL
https://static.getclicky.com/js
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.16.225.240 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
ee5ca5fa7137814c3b2232b406f0bf9d473dcaaaf29949835a4b221ec97c602d

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

last-modified
Thu, 10 Sep 2026 23:27:47 GMT
cache-control
max-age=604800
content-encoding
gzip
cf-cache-status
HIT
age
269005
cf-ray
a3abdc125b8afe97-AMS
x-proxy-cache
MISS
access-control-allow-origin
*
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
text/javascript; charset=utf-8
vary
Accept-Encoding, Accept-Encoding
server
cloudflare
priority
u=3,i=?0
GET
H2
200
logo.png
footyroom.co/pics/
3 KB
4 KB
15ms
14ms
Image
image/png
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://footyroom.co/pics/logo.png
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
91dc55df3cb71d55183ce0f0cacef7f3455f34673d1a433baf045251448c0e66

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000, public
etag
"5d304439-d97"
pragma
public
expires
Wed, 14 Oct 2026 02:11:12 GMT
accept-ranges
bytes
content-length
3479
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
image/png
last-modified
Thu, 18 Jul 2019 10:04:41 GMT
server
nginx
GET
H2
200
2
images.footyroom.com/badges/
5 KB
5 KB
78ms
14ms
Image
image/png
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://images.footyroom.com/badges/2
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
622c4f1f3296bfb04db7db0948903796d7794a19ddb8ade6aed50c309fe1fcb6

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-amz-server-side-encryption
AES256
etag
"14597e4ed94cf663935c3d8b84feca3f"
x-amz-version-id
null
x-amz-request-id
ZB3VWHG8ZSKP66DD
accept-ranges
bytes
x-cache
HIT
content-length
5296
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
image/png
last-modified
Fri, 28 Apr 2023 10:36:46 GMT
server
nginx
x-amz-id-2
L676ChhCRi8R7RKRM0pNI1vgDDbGw5Gdc4fuQvudHxAoRbNHy8Lj9I9/Ly4kriBFD2lDzGN+aGg=
GET
H2
200
215677
images.footyroom.com/badges/
2 KB
2 KB
131ms
85ms
Image
image/gif
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://images.footyroom.com/badges/215677
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
97dd4dda84363c123e3a555000381aebdc578c855bd496e761674011f3654766

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

etag
"1b986cce69fb423601c9ccf5490ab144"
x-amz-version-id
null
x-amz-request-id
RTAEY77XG46F40F0
accept-ranges
bytes
x-cache
REVALIDATED
content-length
1788
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
image/gif
last-modified
Wed, 11 Nov 2015 11:38:01 GMT
server
nginx
x-amz-id-2
6XQQVsPLFEaWOU3HIjMgq1gAtcP/znSBGnpw3UKHpL2rNFPcGU9oBnF01S7PKeB7uaWpi5EXk5Q=
GET
H2
200
f Show response
floors.nitropay.com/
2 B
139 B
172ms
129ms
Fetch
application/json
35.244.144.25
Google LLC
General
Full URL
https://floors.nitropay.com/f?s=2321&c=NL&v=2
Requested by
Host: s.nitropay.com
URL: https://s.nitropay.com/ads-2321.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
35.244.144.25 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
25.144.244.35.bc.googleusercontent.com
Software
/
Resource Hash
44136fa355b3678a1146ad16f7e8649e94fb4fc21fe77e8310c060f61caaff8a

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
via
1.1 google
access-control-allow-origin
*
alt-svc
h3=":443"; ma=2592000
content-length
26
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
application/json
vary
Origin
GET
H2
200
loader.js Show response
srv.scalibur.io/adserver/static/
12 KB
5 KB
56ms
16ms
Script
text/javascript
185.167.98.14
CloudWebManage-EU...
General
Full URL
https://srv.scalibur.io/adserver/static/loader.js
Requested by
Host: s.nitropay.com
URL: https://s.nitropay.com/ads-2321.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
185.167.98.14 Amsterdam, Netherlands, ASN41436 (CloudWebManage-EU Kamatera Inc, US),
Reverse DNS
Software
/
Resource Hash
f782c5428289f6ae64a1aa7a4572b56bdc0b607ce9b1a979396a4e7b8f6dfd9e
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
no-cache, no-store, must-revalidate
content-encoding
gzip
pragma
no-cache
age
0
expires
0
access-control-allow-origin
*
content-length
4517
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
text/javascript
GET
H2
200
ats.js Show response
ats-wrapper.privacymanager.io/ats-modules/438cb908-ed61-41e9-b716-05d5f4122a64/
127 KB
40 KB
87ms
28ms
Script
application/javascript
13.33.187.36
Amazon.com
General
Full URL
https://ats-wrapper.privacymanager.io/ats-modules/438cb908-ed61-41e9-b716-05d5f4122a64/ats.js
Requested by
Host: s.nitropay.com
URL: https://s.nitropay.com/ads-2321.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.33.187.36 New York, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-33-187-36.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
39d17ad943268e4ac1ae837a9e8392803159ea9115dc5f9992fe4589e9787877

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
cache-control
must-revalidate,public,max-age=3600
content-encoding
gzip
x-amz-version-id
xWCQxgGwne3zRw9OaMJGbi2H.JEDKCDU
etag
W/"7406484c1aae9af06caaccc2ca4ad319"
age
537
via
1.1 6ee264f4aa2ef518b13a5a8305e8080e.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
8bG6Bsa-aemV4Y0VGzfWRFiS-yBrAqbkS-X6vq3Jc2QX2xC6RWz3vw==
date
Mon, 14 Sep 2026 02:02:16 GMT
content-type
application/javascript
last-modified
Wed, 02 Sep 2026 06:05:00 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P9
x-amz-server-side-encryption
AES256
GET
H3
200
config.js Show response
cdn.confiant-integrations.net/QwN0KdjTe-a-6y-70Vps9qMqCzM/gpt_and_prebid/
630 KB
123 KB
50ms
23ms
Script
text/javascript
172.64.144.166
Cloudflare
General
Full URL
https://cdn.confiant-integrations.net/QwN0KdjTe-a-6y-70Vps9qMqCzM/gpt_and_prebid/config.js
Requested by
Host: s.nitropay.com
URL: https://s.nitropay.com/ads-2321.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.64.144.166 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
9cbe7017ccc2b87de6f0754ca4b028c9052243ee4419ff648f4585f1787b4f67
Security Headers
Name Value
Strict-Transport-Security max-age=2592000

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
cf-cache-status
HIT
etag
"edd4a770bdecac88e4aa33b563558663"
age
533
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
text/javascript
vary
accept-encoding
last-modified
Mon, 14 Sep 2026 01:45:55 GMT
x-amz-id-2
9nV5KX4+2x6IOb7bNUH3OUh0wUGR9n5s1EhohM6LP89LjPEHcO8WCOXDurbVlMNVIIHEgs0AzKMGfeOGkZljg+v5FKZrd0g4
priority
u=3,i=?0
strict-transport-security
max-age=2592000
cache-control
public, max-age=1100, stale-while-revalidate=3600
x-amz-request-id
H6DJV5BBDAKRSZJZ
cf-ray
a3abdc12599237b0-AMS
accept-ranges
bytes
content-length
125768
server
cloudflare
x-amz-server-side-encryption
AES256
GET
H3
200
gpt.js Show response
securepubads.g.doubleclick.net/tag/js/
125 KB
0
109ms
109ms
Script
text/javascript
142.251.127.156
Google LLC
General
Full URL
https://securepubads.g.doubleclick.net/tag/js/gpt.js
Requested by
Host: s.nitropay.com
URL: https://s.nitropay.com/ads-2321.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.127.156 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfrai-in-f156.1e100.net
Software
cafe /
Resource Hash
fb5290615c75705d27dded2a331aac90e6c5eabba48941bbd78b52c3af158975
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
etag
128 / 20710 / 122880985 / config-hash: 17945051965659213301
x-content-type-options
nosniff
expires
Mon, 14 Sep 2026 02:11:12 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-disposition
attachment; filename="f.txt"
cache-control
private, max-age=900, stale-while-revalidate=3600
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
content-length
38384
x-xss-protection
0
server
cafe
GET
H3
200
ads-video.5c1599a31fce163f0bf0.js
s.nitropay.com/
0
1 KB
27ms
27ms
Other
text/javascript
104.18.3.78
Cloudflare
General
Full URL
https://s.nitropay.com/ads-video.5c1599a31fce163f0bf0.js
Requested by
Host: s.nitropay.com
URL: https://s.nitropay.com/ads-2321.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.18.3.78 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
6ba2ebdb157f9d5409d63533d17a93dd308e702bcb9884573a0a169d8717bf1e
Security Headers
Name Value
Strict-Transport-Security max-age=2592000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Sec-Purpose
prefetch
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
access-control-expose-headers
Content-Type
x-goog-meta-goog-reserved-file-mtime
1789156610
x-goog-hash
crc32c=1agyVA==, md5=7L+2x9ODoOKqKdmkkFyZ0w==
cf-cache-status
HIT
etag
W/"ecbfb6c7d383a0e2aa29d9a4905c99d3"
age
193606
content-encoding
gzip
x-goog-stored-content-encoding
identity
expires
Sat, 11 Sep 2027 20:24:25 GMT
alt-svc
h3=":443"; ma=86400
x-goog-stored-content-length
1005
server-timing
cfExtPri
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
text/javascript
last-modified
Fri, 11 Sep 2026 20:23:34 GMT
priority
u=4,i
x-guploader-uploadid
AJjja9YuqOtX84uavocTFiwjYjC6bcVFUV6H-6mEdhgsQ_v3ZifLBsTMkGuX064xOc7zMNm5LqZ8DM0
strict-transport-security
max-age=2592000; includeSubDomains
cache-control
public, max-age:43200
x-goog-storage-class
MULTI_REGIONAL
cf-ray
a3abdc123bc5fba3-AMS
access-control-allow-origin
*
x-goog-generation
1789158213985188
server
cloudflare
GET
H3
200
ads-standalone.1df6cd936943385c5056.js
s.nitropay.com/
0
3 KB
29ms
29ms
Other
text/javascript
104.18.3.78
Cloudflare
General
Full URL
https://s.nitropay.com/ads-standalone.1df6cd936943385c5056.js
Requested by
Host: s.nitropay.com
URL: https://s.nitropay.com/ads-2321.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.18.3.78 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
7cdf854b7f64ff5d0d42e9aee3b262acfb6c3b319e9f728b471d37d47015ab9a
Security Headers
Name Value
Strict-Transport-Security max-age=2592000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Sec-Purpose
prefetch
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
access-control-expose-headers
Content-Type
x-goog-meta-goog-reserved-file-mtime
1789156610
x-goog-hash
crc32c=jazaRA==, md5=wMzip+A7sNv2OdXcvi6Pqg==
cf-cache-status
HIT
etag
W/"c0cce2a7e03bb0dbf639d5dcbe2e8faa"
age
193606
content-encoding
gzip
x-goog-stored-content-encoding
identity
expires
Sat, 11 Sep 2027 20:24:25 GMT
alt-svc
h3=":443"; ma=86400
x-goog-stored-content-length
8135
server-timing
cfExtPri
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
text/javascript
last-modified
Fri, 11 Sep 2026 20:23:34 GMT
priority
u=4,i
x-guploader-uploadid
AJjja9ZpxPTewo2XnP15vslRAORGo7lvqH5LtxRDegQVmCMJae1gs4mawa3w_TZRfLULoXc9EWjyvVo
strict-transport-security
max-age=2592000; includeSubDomains
cache-control
public, max-age:43200
x-goog-storage-class
MULTI_REGIONAL
cf-ray
a3abdc123bc6fba3-AMS
access-control-allow-origin
*
x-goog-generation
1789158214193762
server
cloudflare
GET
H3
200
1.gif
s.nitropay.com/
42 B
632 B
23ms
22ms
Image
image/gif
104.18.3.78
Cloudflare
General
Full URL
https://s.nitropay.com/1.gif?x=1&adslot=
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.18.3.78 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
Security Headers
Name Value
Strict-Transport-Security max-age=2592000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
3
access-control-expose-headers
Content-Type
x-goog-hash
crc32c=ljrbyA==, md5=2JdGiI2i2VELZKnwMers1Q==
cf-cache-status
HIT
etag
"d89746888da2d9510b64a9f031eaecd5"
age
193605
x-goog-stored-content-encoding
identity
expires
Fri, 18 Sep 2026 20:24:26 GMT
alt-svc
h3=":443"; ma=86400
x-goog-stored-content-length
42
server-timing
cfExtPri
date
Mon, 14 Sep 2026 02:11:12 GMT
x-goog-custom-time
1970-01-01T00:00:00Z
content-type
image/gif
last-modified
Fri, 22 Jan 2021 08:58:45 GMT
priority
u=3,i
x-guploader-uploadid
AJjja9a1xBLunf_h7XITe0oeabRIlNT4JAbIJZrLIELff8VdGjqvJFz-El6i8iuAC5XTwLTu
strict-transport-security
max-age=2592000; includeSubDomains
cache-control
public, max-age=604800
x-goog-meta-
x-goog-storage-class
MULTI_REGIONAL
cf-ray
a3abdc123bc1fba3-AMS
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1611305925409947
content-length
42
server
cloudflare
GET
H2
200
css
fonts.googleapis.com/
10 KB
1 KB
62ms
57ms
Stylesheet
text/css
2a00:1450:4001:c0f::5f
Google LLC
General
Full URL
https://fonts.googleapis.com/css?family=Source+Sans+Pro:300,400%7CRubik:300,400&subset=latin
Requested by
Host: ajax.googleapis.com
URL: https://ajax.googleapis.com/ajax/libs/webfont/1.6.26/webfont.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a00:1450:4001:c0f::5f Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
1d3981e2a7a649628869697e8060bd05d9385b20be2330fc436f4bbab1534694
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-content-type-options
nosniff
expires
Mon, 14 Sep 2026 02:11:12 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
text/css; charset=utf-8
vary
Sec-Fetch-Dest, Sec-Fetch-Mode, Sec-Fetch-Site
last-modified
Mon, 14 Sep 2026 02:11:12 GMT
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=31536000
link
<https://fonts.gstatic.com>; rel=preconnect; crossorigin
cache-control
private, max-age=86400, stale-while-revalidate=604800
timing-allow-origin
*
cross-origin-opener-policy
same-origin-allow-popups
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
x-xss-protection
0
server
ESF
GET
H2
200
bg15.png
cdn.footyroom.co/pics/
88 B
290 B
17ms
17ms
Image
image/png
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://cdn.footyroom.co/pics/bg15.png
Requested by
Host: cdn.footyroom.co
URL: https://cdn.footyroom.co/css/dist/main.89f0a2fe7e05d3174bba.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
221f201b878a88ffb7c038ce5b70ecf20fcb5595557c7ec95f3f491ba42e59f0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://cdn.footyroom.co/css/dist/main.89f0a2fe7e05d3174bba.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000, public
etag
"5d304439-58"
pragma
public
expires
Wed, 14 Oct 2026 02:11:12 GMT
accept-ranges
bytes
content-length
88
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
image/png
last-modified
Thu, 18 Jul 2019 10:04:41 GMT
server
nginx
GET
H2
200
e.js Show response
cdn.traffmovie.com/libs/
8 KB
8 KB
87ms
20ms
Script
application/javascript
178.162.196.143
LEASEWEB-DE-FRA-1...
General
Full URL
https://cdn.traffmovie.com/libs/e.js
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
178.162.196.143 , Germany, ASN28753 (LEASEWEB-DE-FRA-10 Leaseweb Deutschland GmbH, DE),
Reverse DNS
Software
nginx /
Resource Hash
22c197c6555b3b8e701fce02390a145bc268f3d74a4e652c549fd1557f7bac53
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block;

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
1728000
etag
"6a7dea16-1f20"
access-control-allow-methods
GET, OPTIONS
x-content-type-options
nosniff
expires
Tue, 15 Sep 2026 02:11:12 GMT
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
application/javascript; charset=utf-8
last-modified
Thu, 13 Aug 2026 16:00:22 GMT
access-control-allow-headers
X-PINGOTHER
cache-control
max-age=86400
access-control-allow-credentials
true
accept-ranges
bytes
access-control-allow-origin
*
content-length
7968
x-xss-protection
1; mode=block;
server
nginx
POST
H2
200
match:80034717 Show response
footyroom.co/views/
0
224 B
30ms
30ms
XHR
text/html
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://footyroom.co/views/match:80034717
Requested by
Host: ajax.googleapis.com
URL: https://ajax.googleapis.com/ajax/libs/jquery/1.10.2/jquery.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx / PHP/7.3.7-1+0~20190710.40+debian9~1.gbp032aec
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
X-XSRF-TOKEN
steX81dkvMB8jVtXW2TWQXEFpR5vwASOD5SxaqdY
Referer
https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
X-Requested-With
XMLHttpRequest
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Accept
*/*

Response headers

cache-control
no-cache, private
content-encoding
gzip
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
text/html; charset=UTF-8
vary
Accept-Encoding
server
nginx
x-powered-by
PHP/7.3.7-1+0~20190710.40+debian9~1.gbp032aec
GET
H2
200
analytics.js Show response
www.google-analytics.com/
51 KB
21 KB
132ms
39ms
Script
text/javascript
2a00:1450:4001:c13::8a
Google LLC
General
Full URL
https://www.google-analytics.com/analytics.js
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a00:1450:4001:c13::8a Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
Golfe2 /
Resource Hash
f1a61277e3f902f50ab42015d8b07218db9b7601bb0967e54a52bfdcb4fa7e81
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
age
1977
report-to
{"group":"ascnsrsgac:225:0","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/scaffolding/ascnsrsgac:225:0"}],}
x-content-type-options
nosniff
expires
Mon, 14 Sep 2026 03:38:15 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 01:38:15 GMT
last-modified
Tue, 15 Jul 2025 00:44:26 GMT
content-type
text/javascript
vary
Accept-Encoding
strict-transport-security
max-age=31536000; includeSubDomains; preload
cache-control
public, max-age=7200
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
script-src 'none'; form-action 'none'; frame-src 'none'; report-uri https://csp.withgoogle.com/csp/scaffolding/ascnsrsgac:225:0
cross-origin-opener-policy-report-only
same-origin; report-to=ascnsrsgac:225:0
content-length
20802
server
Golfe2
GET
H2
200
icomoon.ttf
cdn.footyroom.co/fonts/
10 KB
10 KB
50ms
15ms
Font
application/octet-stream
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://cdn.footyroom.co/fonts/icomoon.ttf?25
Requested by
Host: cdn.footyroom.co
URL: https://cdn.footyroom.co/css/dist/main.89f0a2fe7e05d3174bba.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
abf75184a8bf40f8ab07d4bb68ab98f778a59e93591cd7e0627b465238e2f6b4

Request headers

Origin
https://footyroom.co
sec-ch-ua-platform
"Linux"
Referer
https://cdn.footyroom.co/css/dist/main.89f0a2fe7e05d3174bba.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000, public
etag
"5d304439-2750"
pragma
public
expires
Wed, 14 Oct 2026 02:11:12 GMT
accept-ranges
bytes
access-control-allow-origin
*
content-length
10064
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
application/octet-stream
last-modified
Thu, 18 Jul 2019 10:04:41 GMT
server
nginx
GET
H2
200
/ Show response
footyroom.co/chat/socket.io/
103 B
243 B
15ms
15ms
XHR
text/plain
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://footyroom.co/chat/socket.io/?EIO=3&transport=polling&t=Q2ThiU2
Requested by
Host: cdnjs.cloudflare.com
URL: https://cdnjs.cloudflare.com/ajax/libs/socket.io/2.2.0/socket.io.slim.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
47ad943b070f25adcb4e1a50ebf5fc0da79a2222ffcefb9d77820cb805a77f71

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Accept
*/*
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

access-control-allow-origin
*
content-length
103
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
text/plain; charset=UTF-8
server
nginx
GET
H2
200
settings Show response
footyroom.co/advertise/
2 B
272 B
30ms
29ms
XHR
application/json
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://footyroom.co/advertise/settings
Requested by
Host: ajax.googleapis.com
URL: https://ajax.googleapis.com/ajax/libs/angularjs/1.5.8/angular.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx / PHP/7.3.7-1+0~20190710.40+debian9~1.gbp032aec
Resource Hash
44136fa355b3678a1146ad16f7e8649e94fb4fc21fe77e8310c060f61caaff8a
Security Headers
Name Value
Strict-Transport-Security max-age=2592000; includeSubDomains
X-Frame-Options sameorigin

Request headers

sec-ch-ua-platform
"Linux"
X-XSRF-TOKEN
steX81dkvMB8jVtXW2TWQXEFpR5vwASOD5SxaqdY
Referer
https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Accept
application/json, text/plain, */*
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=2592000; includeSubDomains
x-powered-by
PHP/7.3.7-1+0~20190710.40+debian9~1.gbp032aec
cache-control
no-cache, private
content-encoding
gzip
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
application/json
vary
Accept-Encoding
server
nginx
x-frame-options
sameorigin
GET
H2
200
ch_4efPW8xc Show response
www.youtube.com/embed/ Frame 6906
151 KB
62 KB
106ms
68ms
Document
text/html
2001:4860:4826:400::
Google LLC
General
Full URL
https://www.youtube.com/embed/ch_4efPW8xc?rel=0
Requested by
Host: ajax.googleapis.com
URL: https://ajax.googleapis.com/ajax/libs/jquery/1.10.2/jquery.min.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:4826:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
b9fe53d3cd2398db8ab734c6f9418f86cfa00bdd5ab00d50339a245c13821386
Security Headers
Name Value
Content-Security-Policy script-src 'unsafe-eval' 'self' 'unsafe-inline' https://www.google.com https://apis.google.com https://ssl.gstatic.com https://www.gstatic.com https://www.googletagmanager.com https://www.google-analytics.com https://*.youtube.com https://*.google.com https://*.gstatic.com https://youtube.com https://www.youtube.com https://google.com https://*.doubleclick.net https://*.googleapis.com https://www.googleadservices.com https://tpc.googlesyndication.com https://www.youtubekids.com https://www.youtube-nocookie.com https://www.youtubeeducation.com https://www-onepick-opensocial.googleusercontent.com;report-uri https://csp.withgoogle.com/csp/youtube_main/allowlist require-trusted-types-for 'script' base-uri 'self';object-src 'none';script-src 'report-sample' 'nonce-9w-yCzTJUS0dfKo2gCx_jA' 'unsafe-inline' 'strict-dynamic' https: http: 'unsafe-eval';report-uri https://csp.withgoogle.com/csp/youtube_main/strict
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://footyroom.co/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cache-control
no-cache, no-store, max-age=0, must-revalidate
content-encoding
br
content-security-policy
script-src 'unsafe-eval' 'self' 'unsafe-inline' https://www.google.com https://apis.google.com https://ssl.gstatic.com https://www.gstatic.com https://www.googletagmanager.com https://www.google-analytics.com https://*.youtube.com https://*.google.com https://*.gstatic.com https://youtube.com https://www.youtube.com https://google.com https://*.doubleclick.net https://*.googleapis.com https://www.googleadservices.com https://tpc.googlesyndication.com https://www.youtubekids.com https://www.youtube-nocookie.com https://www.youtubeeducation.com https://www-onepick-opensocial.googleusercontent.com;report-uri https://csp.withgoogle.com/csp/youtube_main/allowlist require-trusted-types-for 'script' base-uri 'self';object-src 'none';script-src 'report-sample' 'nonce-9w-yCzTJUS0dfKo2gCx_jA' 'unsafe-inline' 'strict-dynamic' https: http: 'unsafe-eval';report-uri https://csp.withgoogle.com/csp/youtube_main/strict
content-type
text/html; charset=utf-8
cross-origin-embedder-policy-report-only
require-corp; report-to="youtube_main"
cross-origin-opener-policy-report-only
same-origin; report-to="youtube_main"
cross-origin-resource-policy
cross-origin
date
Mon, 14 Sep 2026 02:11:12 GMT
expires
Mon, 01 Jan 1990 00:00:00 GMT
origin-trial
AmhMBR6zCLzDDxpW+HfpP67BqwIknWnyMOXOQGfzYswFmJe+fgaI6XZgAzcxOrzNtP7hEDsOo1jdjFnVr2IdxQ4AAAB4eyJvcmlnaW4iOiJodHRwczovL3lvdXR1YmUuY29tOjQ0MyIsImZlYXR1cmUiOiJXZWJWaWV3WFJlcXVlc3RlZFdpdGhEZXByZWNhdGlvbiIsImV4cGlyeSI6MTc1ODA2NzE5OSwiaXNTdWJkb21haW4iOnRydWV9 AiDEBptUfVeO93q48VdVMe/ubupazdAl8AaHP+NBzdnW8quUcHdzJUyGSfrmtpKJu7EOvwRp9ug2rEo3XU+WMAMAAAB2eyJvcmlnaW4iOiJodHRwczovL3lvdXR1YmUuY29tOjQ0MyIsImZlYXR1cmUiOiJEZXZpY2VCb3VuZFNlc3Npb25DcmVkZW50aWFsczIiLCJleHBpcnkiOjE3NzQzMTA0MDAsImlzU3ViZG9tYWluIjp0cnVlfQ==
p3p
CP="This is not a P3P policy! See http://support.google.com/accounts/answer/151657?hl=nl for more info."
permissions-policy
ch-ua-arch=*, ch-ua-bitness=*, ch-ua-full-version=*, ch-ua-full-version-list=*, ch-ua-model=*, ch-ua-wow64=*, ch-ua-form-factors=*, ch-ua-platform=*, ch-ua-platform-version=*
pragma
no-cache
report-to
{"group":"youtube_main","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube_main"}]}
server
ESF
strict-transport-security
max-age=31536000
vary
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
x-content-type-options
nosniff
x-xss-protection
0
GET
H2
200
formations.html Show response
footyroom.co/views/ng/formations/
6 KB
2 KB
16ms
15ms
XHR
text/html
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://footyroom.co/views/ng/formations/formations.html?17
Requested by
Host: ajax.googleapis.com
URL: https://ajax.googleapis.com/ajax/libs/angularjs/1.5.8/angular.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
41bde1003b9ce5cb663e859474f0c982ce1985c6012710343704e05c1b7072e8

Request headers

sec-ch-ua-platform
"Linux"
X-XSRF-TOKEN
steX81dkvMB8jVtXW2TWQXEFpR5vwASOD5SxaqdY
Referer
https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Accept
application/json, text/plain, */*
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
date
Mon, 14 Sep 2026 02:11:12 GMT
etag
W/"5dfb3cbd-192b"
content-type
text/html
last-modified
Thu, 19 Dec 2019 09:02:53 GMT
server
nginx
vary
Accept-Encoding
GET
H2
200
grid-pattern-2.png
cdn.footyroom.co/pics/
300 B
503 B
17ms
14ms
Image
image/png
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://cdn.footyroom.co/pics/grid-pattern-2.png
Requested by
Host: cdn.footyroom.co
URL: https://cdn.footyroom.co/css/dist/main.89f0a2fe7e05d3174bba.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
fcd1c1681d6488b333808eacb9b6941182e5ddb72aebb063d107b9ebde67b17e

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://cdn.footyroom.co/css/dist/main.89f0a2fe7e05d3174bba.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000, public
etag
"5d304439-12c"
pragma
public
expires
Wed, 14 Oct 2026 02:11:12 GMT
accept-ranges
bytes
content-length
300
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
image/png
last-modified
Thu, 18 Jul 2019 10:04:41 GMT
server
nginx
GET
H2
200
fabric-bg.jpg
cdn.footyroom.co/pics/
15 KB
15 KB
17ms
15ms
Image
image/jpeg
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://cdn.footyroom.co/pics/fabric-bg.jpg
Requested by
Host: cdn.footyroom.co
URL: https://cdn.footyroom.co/css/dist/main.89f0a2fe7e05d3174bba.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
adacc49bf84c6e75cfe776430e55282e25b96c51bd4a0f338264322f8b8fcbd3

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://cdn.footyroom.co/css/dist/main.89f0a2fe7e05d3174bba.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000, public
etag
"5d304439-3b82"
pragma
public
expires
Wed, 14 Oct 2026 02:11:12 GMT
accept-ranges
bytes
content-length
15234
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
image/jpeg
last-modified
Thu, 18 Jul 2019 10:04:41 GMT
server
nginx
GET
H2
200
icons.png
cdn.footyroom.co/pics/
5 KB
5 KB
22ms
19ms
Image
image/png
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://cdn.footyroom.co/pics/icons.png?v=11
Requested by
Host: cdn.footyroom.co
URL: https://cdn.footyroom.co/css/dist/main.89f0a2fe7e05d3174bba.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
fbc67f7bea33a2ee53e323413356f14a4b5071afab74154afab744a1ccaaa40c

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://cdn.footyroom.co/css/dist/main.89f0a2fe7e05d3174bba.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000, public
etag
"5d304439-1464"
pragma
public
expires
Wed, 14 Oct 2026 02:11:12 GMT
accept-ranges
bytes
content-length
5220
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
image/png
last-modified
Thu, 18 Jul 2019 10:04:41 GMT
server
nginx
GET
H2
200
maxresdefault.jpg
i.ytimg.com/vi/ch_4efPW8xc/
168 KB
168 KB
153ms
61ms
Image
image/jpeg
2a00:1450:4001:c15::77
Google LLC
General
Full URL
https://i.ytimg.com/vi/ch_4efPW8xc/maxresdefault.jpg
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a00:1450:4001:c15::77 Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
7de3c31102bcdca0518cfe683d5ebde8774aa00b726578d55ab513c13bbc5b07
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

etag
"1789080398"
age
0
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Mon, 14 Sep 2026 04:11:12 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
image/jpeg
cache-control
public, max-age=7200
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
171618
x-xss-protection
0
server
sffe
GET
H2
200
maxresdefault.jpg
i.ytimg.com/vi/54u-qUk_xek/
176 KB
176 KB
142ms
50ms
Image
image/jpeg
2a00:1450:4001:c15::77
Google LLC
General
Full URL
https://i.ytimg.com/vi/54u-qUk_xek/maxresdefault.jpg
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a00:1450:4001:c15::77 Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
fd6abf9e359db95ceba2295b57c529f60a6280d6c0be29e0636f763e6f7d6a09
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

etag
"1789081381"
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Mon, 14 Sep 2026 04:11:12 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
image/jpeg
cache-control
public, max-age=7200
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
179941
x-xss-protection
0
server
sffe
GET
H2
200
maxresdefault.jpg
i.ytimg.com/vi/3bntMP-pjYo/
156 KB
157 KB
310ms
226ms
Image
image/jpeg
2a00:1450:4001:c15::77
Google LLC
General
Full URL
https://i.ytimg.com/vi/3bntMP-pjYo/maxresdefault.jpg
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a00:1450:4001:c15::77 Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
d9647ecef74eb4b95dee684b8e64f746c1cc25531507fdc230323944ca3a5acd
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

etag
"1789079374"
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Mon, 14 Sep 2026 04:11:12 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
image/jpeg
cache-control
public, max-age=7200
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
160244
x-xss-protection
0
server
sffe
GET
H2
200
maxresdefault.jpg
i.ytimg.com/vi/STY6Ec-nJlc/
209 KB
209 KB
258ms
182ms
Image
image/jpeg
2a00:1450:4001:c15::77
Google LLC
General
Full URL
https://i.ytimg.com/vi/STY6Ec-nJlc/maxresdefault.jpg
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a00:1450:4001:c15::77 Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
024a9fdfcbe8e3062bde5451967c598720afa912cfc409196973d5cd5afb3165
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

etag
"1789077746"
age
0
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Mon, 14 Sep 2026 04:11:12 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
image/jpeg
cache-control
public, max-age=7200
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
213914
x-xss-protection
0
server
sffe
GET
H2
200
spinner.svg
cdn.footyroom.co/pics/
2 KB
2 KB
17ms
16ms
Image
image/svg+xml
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://cdn.footyroom.co/pics/spinner.svg
Requested by
Host: cdn.footyroom.co
URL: https://cdn.footyroom.co/css/dist/main.89f0a2fe7e05d3174bba.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
4ca933d11ea854b96a4e68074962248402e5ac3e71b1ff4b8aac7c81485f8ebb

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://cdn.footyroom.co/css/dist/main.89f0a2fe7e05d3174bba.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000, public
etag
"5d304439-799"
pragma
public
expires
Wed, 14 Oct 2026 02:11:12 GMT
accept-ranges
bytes
content-length
1945
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
image/svg+xml
last-modified
Thu, 18 Jul 2019 10:04:41 GMT
server
nginx
GET
H2
200
footer_logo.png
cdn.footyroom.co/pics/
3 KB
4 KB
18ms
17ms
Image
image/png
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://cdn.footyroom.co/pics/footer_logo.png
Requested by
Host: cdn.footyroom.co
URL: https://cdn.footyroom.co/css/dist/main.89f0a2fe7e05d3174bba.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
6bab55ba848dbc6da9af1a8b805f4c9d551b503f0c3f077a04dffba5b03d6372

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://cdn.footyroom.co/css/dist/main.89f0a2fe7e05d3174bba.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000, public
etag
"5d304439-d55"
pragma
public
expires
Wed, 14 Oct 2026 02:11:12 GMT
accept-ranges
bytes
content-length
3413
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
image/png
last-modified
Thu, 18 Jul 2019 10:04:41 GMT
server
nginx
GET
H2
200
social-sprite.png
cdn.footyroom.co/pics/
5 KB
5 KB
19ms
18ms
Image
image/png
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://cdn.footyroom.co/pics/social-sprite.png?3
Requested by
Host: cdn.footyroom.co
URL: https://cdn.footyroom.co/css/dist/main.89f0a2fe7e05d3174bba.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
d2fdf0ea6e97d087e55c19447a2a212ab027724b8a731e1878c567d8c1b51394

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://cdn.footyroom.co/css/dist/main.89f0a2fe7e05d3174bba.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000, public
etag
"5d304439-14a2"
pragma
public
expires
Wed, 14 Oct 2026 02:11:12 GMT
accept-ranges
bytes
content-length
5282
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
image/png
last-modified
Thu, 18 Jul 2019 10:04:41 GMT
server
nginx
GET
H3
200
6xKydSBYKcSV-LCoeQqfX1RYOo3ik4zwlxdu.woff2
fonts.gstatic.com/s/sourcesanspro/v23/
14 KB
14 KB
105ms
57ms
Font
font/woff2
142.250.154.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/sourcesanspro/v23/6xKydSBYKcSV-LCoeQqfX1RYOo3ik4zwlxdu.woff2
Requested by
Host: fonts.googleapis.com
URL: https://fonts.googleapis.com/css?family=Source+Sans+Pro:300,400%7CRubik:300,400&subset=latin
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.250.154.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bt-in-f94.1e100.net
Software
sffe /
Resource Hash
46d6a0984aa795b764141232671160e61bdcc49e900de67ca6b35bae25b1ebdd
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://footyroom.co
sec-ch-ua-platform
"Linux"
Referer
https://fonts.googleapis.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

age
207309
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Sat, 11 Sep 2027 16:36:03 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 11 Sep 2026 16:36:03 GMT
last-modified
Wed, 10 Sep 2025 16:47:45 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
14792
x-xss-protection
0
server
sffe
GET
H3
200
6xK3dSBYKcSV-LCoeQqfX1RYOo3qOK7l.woff2
fonts.gstatic.com/s/sourcesanspro/v23/
15 KB
15 KB
93ms
45ms
Font
font/woff2
142.250.154.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/sourcesanspro/v23/6xK3dSBYKcSV-LCoeQqfX1RYOo3qOK7l.woff2
Requested by
Host: fonts.googleapis.com
URL: https://fonts.googleapis.com/css?family=Source+Sans+Pro:300,400%7CRubik:300,400&subset=latin
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.250.154.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bt-in-f94.1e100.net
Software
sffe /
Resource Hash
691491f1fc8badab623e1be56f92cc2d98c462b16617c67e1e288d6b061444bc
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://footyroom.co
sec-ch-ua-platform
"Linux"
Referer
https://fonts.googleapis.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

age
212189
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Sat, 11 Sep 2027 15:14:43 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 11 Sep 2026 15:14:43 GMT
last-modified
Wed, 10 Sep 2025 16:47:45 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
14868
x-xss-protection
0
server
sffe
GET
H3
200
iJWKBXyIfDnIV7nBrXw.woff2
fonts.gstatic.com/s/rubik/v31/
35 KB
35 KB
87ms
40ms
Font
font/woff2
142.250.154.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/rubik/v31/iJWKBXyIfDnIV7nBrXw.woff2
Requested by
Host: fonts.googleapis.com
URL: https://fonts.googleapis.com/css?family=Source+Sans+Pro:300,400%7CRubik:300,400&subset=latin
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.250.154.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bt-in-f94.1e100.net
Software
sffe /
Resource Hash
691cd1d9b4c0cdf31a1dcf04259c86f92c85e69f6622abab7964d81e36890691
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://footyroom.co
sec-ch-ua-platform
"Linux"
Referer
https://fonts.googleapis.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

age
206046
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Sat, 11 Sep 2027 16:57:06 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 11 Sep 2026 16:57:06 GMT
last-modified
Tue, 09 Sep 2025 18:32:10 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
35348
x-xss-protection
0
server
sffe
POST
H2
200
/ Show response
footyroom.co/chat/socket.io/
2 B
169 B
17ms
16ms
XHR
text/html
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://footyroom.co/chat/socket.io/?EIO=3&transport=polling&t=Q2ThiV4&sid=2RYDuym3aogoqiIXAlnK
Requested by
Host: cdnjs.cloudflare.com
URL: https://cdnjs.cloudflare.com/ajax/libs/socket.io/2.2.0/socket.io.slim.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
2689367b205c16ce32ed4200942b8b8b1e262dfc70d9bc9fbc77c49699a4f1df

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Accept
*/*
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

access-control-allow-origin
https://footyroom.co
content-length
2
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
text/html
server
nginx
access-control-allow-credentials
true
GET
H2
200
/ Show response
footyroom.co/chat/socket.io/
26 B
165 B
18ms
18ms
XHR
text/plain
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://footyroom.co/chat/socket.io/?EIO=3&transport=polling&t=Q2ThiV5&sid=2RYDuym3aogoqiIXAlnK
Requested by
Host: cdnjs.cloudflare.com
URL: https://cdnjs.cloudflare.com/ajax/libs/socket.io/2.2.0/socket.io.slim.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
f318f161fb4354b77bc6a4f6086f1312b5da3991aab2668ed6e993d166928d14

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Accept
*/*
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

access-control-allow-origin
*
content-length
26
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
text/plain; charset=UTF-8
server
nginx
GET
H2
200
poll.html Show response
footyroom.co/views/ng/motm/
763 B
505 B
14ms
14ms
XHR
text/html
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://footyroom.co/views/ng/motm/poll.html?1
Requested by
Host: ajax.googleapis.com
URL: https://ajax.googleapis.com/ajax/libs/angularjs/1.5.8/angular.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
c1b06365cc2fa5aa50277d4bfb723abb6515435e92582144e9ff208c8be6b2e3

Request headers

sec-ch-ua-platform
"Linux"
X-XSRF-TOKEN
steX81dkvMB8jVtXW2TWQXEFpR5vwASOD5SxaqdY
Referer
https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Accept
application/json, text/plain, */*
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
date
Mon, 14 Sep 2026 02:11:12 GMT
etag
W/"5d304439-2fb"
content-type
text/html
last-modified
Thu, 18 Jul 2019 10:04:41 GMT
server
nginx
vary
Accept-Encoding
GET
H2
200
field-hz.png
cdn.footyroom.co/pics/
24 KB
24 KB
14ms
14ms
Image
image/png
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://cdn.footyroom.co/pics/field-hz.png?v=9
Requested by
Host: cdn.footyroom.co
URL: https://cdn.footyroom.co/css/dist/main.89f0a2fe7e05d3174bba.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
65fdf886bd4624b31647215def1ee1bb13c56557f180e8689f4070f23247b08d

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://cdn.footyroom.co/css/dist/main.89f0a2fe7e05d3174bba.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000, public
etag
"5d304439-5fe1"
pragma
public
expires
Wed, 14 Oct 2026 02:11:12 GMT
accept-ranges
bytes
content-length
24545
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
image/png
last-modified
Thu, 18 Jul 2019 10:04:41 GMT
server
nginx
POST
H2
200
/ Show response
footyroom.co/chat/socket.io/
2 B
169 B
15ms
14ms
XHR
text/html
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://footyroom.co/chat/socket.io/?EIO=3&transport=polling&t=Q2ThiY7&sid=2RYDuym3aogoqiIXAlnK
Requested by
Host: cdnjs.cloudflare.com
URL: https://cdnjs.cloudflare.com/ajax/libs/socket.io/2.2.0/socket.io.slim.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
2689367b205c16ce32ed4200942b8b8b1e262dfc70d9bc9fbc77c49699a4f1df

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Accept
*/*
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

access-control-allow-origin
https://footyroom.co
content-length
2
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
text/html
server
nginx
access-control-allow-credentials
true
GET
H2
200
/ Show response
footyroom.co/chat/socket.io/
21 B
160 B
22ms
22ms
XHR
text/plain
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://footyroom.co/chat/socket.io/?EIO=3&transport=polling&t=Q2ThiY7.0&sid=2RYDuym3aogoqiIXAlnK
Requested by
Host: cdnjs.cloudflare.com
URL: https://cdnjs.cloudflare.com/ajax/libs/socket.io/2.2.0/socket.io.slim.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
380da8311b69d9d978d9219e8547a526d75d873d5e0ac5a2bbdc5bb0da01f960

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Accept
*/*
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

access-control-allow-origin
*
content-length
21
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
text/plain; charset=UTF-8
server
nginx
GET
H2
200
www-player.css
www.youtube.com/s/player/8c3fda2d/ Frame 6906
531 KB
57 KB
16ms
12ms
Stylesheet
text/css
2001:4860:4826:400::
Google LLC
General
Full URL
https://www.youtube.com/s/player/8c3fda2d/www-player.css
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/ch_4efPW8xc?rel=0
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:4826:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
1e6f131e5c23998532caa01dec741cd746efdb7364cffaf33a43f227aaa0d458
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/ch_4efPW8xc?rel=0
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
50523
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Mon, 13 Sep 2027 12:09:09 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Sun, 13 Sep 2026 12:09:09 GMT
last-modified
Mon, 07 Sep 2026 04:37:27 GMT
content-type
text/css
vary
Accept-Encoding, Origin
cache-control
public, max-age=31536000
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
58390
x-xss-protection
0
server
sffe
GET
H2
200
m=root,base
www.youtube.com/s/_/ytembeds/_/ss/k=ytembeds.base.HY7wD9GGp-g.L.W.O/am=AAAAQA/d=1/br=1/rs=AGKMywE4Kjs9hFDhD74lwcLYIXdA_OMvQQ/ Frame 6906
0
409 B
24ms
21ms
Stylesheet
text/css
2001:4860:4826:400::
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/ss/k=ytembeds.base.HY7wD9GGp-g.L.W.O/am=AAAAQA/d=1/br=1/rs=AGKMywE4Kjs9hFDhD74lwcLYIXdA_OMvQQ/m=root,base
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/ch_4efPW8xc?rel=0
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:4826:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/ch_4efPW8xc?rel=0
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

age
220068
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Sat, 11 Sep 2027 13:03:24 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 11 Sep 2026 13:03:24 GMT
last-modified
Fri, 11 Sep 2026 03:12:40 GMT
content-type
text/css; charset=UTF-8
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
0
x-xss-protection
0
server
sffe
GET
H2
200
m=root,base Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywHdVJjs6ktwWXG8Pg3CpN4ZEVjBaQ/ Frame 6906
456 KB
155 KB
25ms
22ms
Script
text/javascript
2001:4860:4826:400::
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywHdVJjs6ktwWXG8Pg3CpN4ZEVjBaQ/m=root,base
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/ch_4efPW8xc?rel=0
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:4826:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
555e95e5af65cfd867790ac83d0f93780e6a63078135648b21c4fb935c1e04b0
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/ch_4efPW8xc?rel=0
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
220068
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Sat, 11 Sep 2027 13:03:24 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 11 Sep 2026 13:03:24 GMT
last-modified
Fri, 11 Sep 2026 09:12:02 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
158737
x-xss-protection
0
server
sffe
GET
H2
200
base.js Show response
www.youtube.com/s/player/8c3fda2d/player_embed_es6.vflset/nl_NL/ Frame 6906
2 MB
473 KB
46ms
43ms
Script
text/javascript
2001:4860:4826:400::
Google LLC
General
Full URL
https://www.youtube.com/s/player/8c3fda2d/player_embed_es6.vflset/nl_NL/base.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/ch_4efPW8xc?rel=0
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:4826:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
a5cc31c26956638a4a4039d99aa5ca121d1325d9938c3449bca213f9a7fc3b8f
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/ch_4efPW8xc?rel=0
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
262618
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Sat, 11 Sep 2027 01:14:14 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 11 Sep 2026 01:14:14 GMT
last-modified
Mon, 07 Sep 2026 04:37:27 GMT
content-type
text/javascript
vary
Accept-Encoding, Origin
cache-control
public, max-age=31536000
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
483618
x-xss-protection
0
server
sffe
GET
H3
200
KFO7CnqEu92Fr1ME7kSn66aGLdTylUAMa3yUBA.woff2
fonts.gstatic.com/s/roboto/v48/ Frame 6906
39 KB
39 KB
85ms
39ms
Font
font/woff2
142.250.154.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/roboto/v48/KFO7CnqEu92Fr1ME7kSn66aGLdTylUAMa3yUBA.woff2
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/ch_4efPW8xc?rel=0
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.250.154.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bt-in-f94.1e100.net
Software
sffe /
Resource Hash
20b535fa80c8189e3b87d1803038389960203a886d502bc2ef1857affc2f38d2
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://www.youtube.com
sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

age
206048
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Sat, 11 Sep 2027 16:57:04 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 11 Sep 2026 16:57:04 GMT
last-modified
Thu, 29 May 2025 23:30:55 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
40128
x-xss-protection
0
server
sffe
POST
H3
204
AGSKWxXcIhhbiu358SLpLSZn6QOYaPbwlxav7jRknBPngNDhiu-aHpWWnD2iRf3rbMleS48-7r4S1XoPT6c4gZz2exbyv7UHl-eY0YIPBUvEy2yfJ-HmYY3As4TrqkAoX_Vlr7ImJsCCaQ== Show response
fundingchoicesmessages.google.com/el/
0
28 B
104ms
56ms
XHR
text/html
142.251.110.100
Google LLC
General
Full URL
https://fundingchoicesmessages.google.com/el/AGSKWxXcIhhbiu358SLpLSZn6QOYaPbwlxav7jRknBPngNDhiu-aHpWWnD2iRf3rbMleS48-7r4S1XoPT6c4gZz2exbyv7UHl-eY0YIPBUvEy2yfJ-HmYY3As4TrqkAoX_Vlr7ImJsCCaQ==
Requested by
Host:
URL: /_/mss/boq-content-ads-contributor/_/js/k=boq-content-ads-contributor.ContributorServingResponseClientJs.nl.vyMVZXSm2Sw.es5.O/d=1/rs=AJlcJMwT-z7-Ua2kRQtmTjsz1eye77FxMQ/m=kernel_loader,loader_js_executable
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.110.100 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f100.1e100.net
Software
ESF /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Content-Security-Policy script-src 'report-sample' 'nonce-pLJXD9odlxlHLJ_z3qIIsQ' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/ContributorLoggingHttp/cspreport;worker-src 'self', script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/ContributorLoggingHttp/cspreport/allowlist, require-trusted-types-for 'script';report-uri /_/ContributorLoggingHttp/cspreport
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
text/plain
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
86400
access-control-allow-methods
POST, GET, OPTIONS
x-content-type-options
nosniff
expires
Mon, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
text/html; charset=utf-8
x-frame-options
SAMEORIGIN
reporting-endpoints
default="/_/ContributorLoggingHttp/web-reports?context=eJzj0tDikmJw1pBi-FB_mfUHEC-cFsi2EohFDILYZIA47WA4Wx4QC_FwHFg_9yqbQMfWq8-ZlFyS8gvjk_PzSlLzSnQTU4p1QeyizKTSkvwiFHZqGUhFTn56emZeeryRgZGZgaWBpZ6hQXyBAQDaYSxL"
content-security-policy
script-src 'report-sample' 'nonce-pLJXD9odlxlHLJ_z3qIIsQ' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/ContributorLoggingHttp/cspreport;worker-src 'self', script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/ContributorLoggingHttp/cspreport/allowlist, require-trusted-types-for 'script';report-uri /_/ContributorLoggingHttp/cspreport
cache-control
no-cache, no-store, max-age=0, must-revalidate
cross-origin-opener-policy
same-origin
pragma
no-cache
accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
access-control-allow-credentials
true
permissions-policy
ch-ua-arch=*, ch-ua-bitness=*, ch-ua-full-version=*, ch-ua-full-version-list=*, ch-ua-model=*, ch-ua-wow64=*, ch-ua-form-factors=*, ch-ua-platform=*, ch-ua-platform-version=*
access-control-allow-origin
https://footyroom.co
content-length
0
x-xss-protection
0
server
ESF
POST
H3
204
AGSKWxXcIhhbiu358SLpLSZn6QOYaPbwlxav7jRknBPngNDhiu-aHpWWnD2iRf3rbMleS48-7r4S1XoPT6c4gZz2exbyv7UHl-eY0YIPBUvEy2yfJ-HmYY3As4TrqkAoX_Vlr7ImJsCCaQ== Show response
fundingchoicesmessages.google.com/el/
0
28 B
143ms
96ms
XHR
text/html
142.251.110.100
Google LLC
General
Full URL
https://fundingchoicesmessages.google.com/el/AGSKWxXcIhhbiu358SLpLSZn6QOYaPbwlxav7jRknBPngNDhiu-aHpWWnD2iRf3rbMleS48-7r4S1XoPT6c4gZz2exbyv7UHl-eY0YIPBUvEy2yfJ-HmYY3As4TrqkAoX_Vlr7ImJsCCaQ==
Requested by
Host:
URL: /_/mss/boq-content-ads-contributor/_/js/k=boq-content-ads-contributor.ContributorServingResponseClientJs.nl.vyMVZXSm2Sw.es5.O/d=1/rs=AJlcJMwT-z7-Ua2kRQtmTjsz1eye77FxMQ/m=kernel_loader,loader_js_executable
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.110.100 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f100.1e100.net
Software
ESF /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script';report-uri /_/ContributorLoggingHttp/cspreport, script-src 'report-sample' 'nonce-nttjjyFAadSMn7W-s5m32Q' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/ContributorLoggingHttp/cspreport;worker-src 'self', script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/ContributorLoggingHttp/cspreport/allowlist
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
text/plain
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
86400
access-control-allow-methods
POST, GET, OPTIONS
x-content-type-options
nosniff
expires
Mon, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
text/html; charset=utf-8
x-frame-options
SAMEORIGIN
reporting-endpoints
default="/_/ContributorLoggingHttp/web-reports?context=eJzj0tDikmII0pBi-FB_mfUHEC-cFsi2EohFDILYZIA47WA4Wx4QC_FwHFg_9yqbwI7ZJ38xKbkk5RfGJ-fnlaTmlegmphTrgthFmUmlJflFKOzUMpCKnPz09My89HgjAyMzA0sDSz1Dg_gCAwDp4Sx3"
content-security-policy
require-trusted-types-for 'script';report-uri /_/ContributorLoggingHttp/cspreport, script-src 'report-sample' 'nonce-nttjjyFAadSMn7W-s5m32Q' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/ContributorLoggingHttp/cspreport;worker-src 'self', script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/ContributorLoggingHttp/cspreport/allowlist
cache-control
no-cache, no-store, max-age=0, must-revalidate
cross-origin-opener-policy
same-origin
pragma
no-cache
accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
access-control-allow-credentials
true
permissions-policy
ch-ua-arch=*, ch-ua-bitness=*, ch-ua-full-version=*, ch-ua-full-version-list=*, ch-ua-model=*, ch-ua-wow64=*, ch-ua-form-factors=*, ch-ua-platform=*, ch-ua-platform-version=*
access-control-allow-origin
https://footyroom.co
content-length
0
x-xss-protection
0
server
ESF
GET
H2
200
AGSKWxXBSOP279aZAHMQMosEkqPlInjTTRcmh6eRy1bJ4wqeRUtvlGSVnui102nr1NIYQTxmWKzbJt3kC1nkoonW5e54iW-pVlkORP0fD1WLSwzXfAMGyN_ldne7WJ8NC5uMw9MaL2IyFg== Show response
fundingchoicesmessages.google.com/f/
9 KB
4 KB
66ms
64ms
Script
application/javascript
2a00:1450:4001:c15::66
Google LLC
General
Full URL
https://fundingchoicesmessages.google.com/f/AGSKWxXBSOP279aZAHMQMosEkqPlInjTTRcmh6eRy1bJ4wqeRUtvlGSVnui102nr1NIYQTxmWKzbJt3kC1nkoonW5e54iW-pVlkORP0fD1WLSwzXfAMGyN_ldne7WJ8NC5uMw9MaL2IyFg==?fccs=W251bGwsbnVsbCxudWxsLG51bGwsbnVsbCxudWxsLFsxNzg5MzUxODcyLDcwMDAwMDAwMF0sbnVsbCxudWxsLG51bGwsW251bGwsWzddXSwiaHR0cHM6Ly9mb290eXJvb20uY28vbWF0Y2hlcy84MDAzNDcxNy9tYW5jaGVzdGVyLXVuaXRlZC12cy1zYWJhaC1may9yZXZpZXciLG51bGwsW1s4LCJ2eU1WWlhTbTJTdyJdLFs5LCJubCJdLFszNSwiMTc4OTM1MTg3MiJdLFsxOSwiMiJdLFsyNCwiIl0sWzI5LCJmYWxzZSJdXV0
Requested by
Host:
URL: /_/mss/boq-content-ads-contributor/_/js/k=boq-content-ads-contributor.ContributorServingResponseClientJs.nl.vyMVZXSm2Sw.es5.O/d=1/rs=AJlcJMwT-z7-Ua2kRQtmTjsz1eye77FxMQ/m=kernel_loader,loader_js_executable
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a00:1450:4001:c15::66 Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
d456c1206018ff3e37711aa22b2118e5f9f9985be3e7fc9567cb76e02c4e3501
Security Headers
Name Value
Content-Security-Policy script-src 'report-sample' 'nonce-hSPe0BQR8jMqVayyCnOIrw' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/ContributorServingWebSwitchboardHttp/cspreport;worker-src 'self', script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/ContributorServingWebSwitchboardHttp/cspreport/allowlist, require-trusted-types-for 'script';report-uri /_/ContributorServingWebSwitchboardHttp/cspreport
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-content-type-options
nosniff
expires
Mon, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
application/javascript; charset=utf-8
x-frame-options
SAMEORIGIN
reporting-endpoints
default="/_/ContributorServingWebSwitchboardHttp/web-reports?context=eJzjytHikmLw1ZBiOHnrNtNFIG69eY51OhCXLDrP2gbEXUA8B4gNFS6xOgPxh_rLrD-AuEjiCmsLEH-qusEqUn2D9VuxLxtHiS8by1t_toXTAtlWArGIQRCbDBCnHQxnywNiIR6OA-vnXmUT6Ljz7C6TkkZSfmF8cn5eSVFmUmlJflFaclpqcWpRWWpRvJGBkZmBpYGlnqFhfIEBAAYtQDM"
content-security-policy
script-src 'report-sample' 'nonce-hSPe0BQR8jMqVayyCnOIrw' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/ContributorServingWebSwitchboardHttp/cspreport;worker-src 'self', script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/ContributorServingWebSwitchboardHttp/cspreport/allowlist, require-trusted-types-for 'script';report-uri /_/ContributorServingWebSwitchboardHttp/cspreport
cache-control
no-cache, no-store, max-age=0, must-revalidate
timing-allow-origin
*
cross-origin-opener-policy
same-origin
pragma
no-cache
accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
cross-origin-resource-policy
cross-origin
permissions-policy
ch-ua-arch=*, ch-ua-bitness=*, ch-ua-full-version=*, ch-ua-full-version-list=*, ch-ua-model=*, ch-ua-wow64=*, ch-ua-form-factors=*, ch-ua-platform=*, ch-ua-platform-version=*
x-xss-protection
0
server
ESF
GET
H2
200
/ Show response
footyroom.co/chat/socket.io/
26 B
165 B
18ms
17ms
XHR
text/plain
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://footyroom.co/chat/socket.io/?EIO=3&transport=polling&t=Q2ThiZ4&sid=2RYDuym3aogoqiIXAlnK
Requested by
Host: cdnjs.cloudflare.com
URL: https://cdnjs.cloudflare.com/ajax/libs/socket.io/2.2.0/socket.io.slim.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
94c23c75d87c8af7ad4ab772d42c45f78c44bd9c99b89b0d512296aef53bb757

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Accept
*/*
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

access-control-allow-origin
*
content-length
26
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
text/plain; charset=UTF-8
server
nginx
GET
H2
200
/ Show response
ui.cleverwebserver.com/
248 B
435 B
50ms
39ms
Script
application/javascript
2606:4700:4405::6812:21f7
Cloudflare
General
Full URL
https://ui.cleverwebserver.com/
Requested by
Host: scripts.cleverwebserver.com
URL: https://scripts.cleverwebserver.com/746d84c846e7a9d594919df4eab520e7.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2606:4700:4405::6812:21f7 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
b2d9eab8aa663fec87b5869aa1e13e45c2bd8e125b4dcfdc10b07f7f6179791d

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

access-control-expose-headers
*
content-encoding
br
cf-cache-status
DYNAMIC
access-control-allow-methods
GET, PUT, POST, DELETE, PATCH, OPTIONS
cf-ray
a3abdc14ae93285a-AMS
access-control-allow-origin
*
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
application/javascript
server
cloudflare
access-control-allow-headers
DNT,Keep-Alive,User-Agent,X-Requested-With,If-Modified-Since,Cache-Control,Content-Type,Range,Authorization
GET
H3
200
wrap.js Show response
cdn.confiant-integrations.net/gptprebidnative/202609031720/
408 KB
144 KB
20ms
19ms
Script
application/javascript
172.64.144.166
Cloudflare
General
Full URL
https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/QwN0KdjTe-a-6y-70Vps9qMqCzM/gpt_and_prebid/config.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.64.144.166 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
94d264bd436b015615096ddd81b9ea69a29930139d2a4231232c27a936704ca5
Security Headers
Name Value
Strict-Transport-Security max-age=2592000

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
cf-cache-status
HIT
etag
"7813897c38c2201d27cf7934e1e045ac"
age
905710
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
application/javascript; charset=utf-8
vary
accept-encoding
last-modified
Thu, 03 Sep 2026 14:24:03 GMT
x-amz-id-2
QPSLLFiqBZ9uqbBfoAZvpFQukp0utbhcEmPTIudphYsxW2ePRRaVYW+lMyMcmxJdkgaCf+QnZOE=
priority
u=3,i=?0
strict-transport-security
max-age=2592000
cache-control
public, max-age=31536000
x-amz-request-id
6WJNTXGEJFVBG20D
cf-ray
a3abdc14dea137b0-AMS
accept-ranges
bytes
content-length
146552
server
cloudflare
x-amz-server-side-encryption
AES256
GET
H3
200
config.js Show response
cdn.confiant-integrations.net/IKOzVPjtHv3tevs-RDaJOMdtkBI/video/
355 KB
73 KB
34ms
33ms
Script
text/javascript
172.64.144.166
Cloudflare
General
Full URL
https://cdn.confiant-integrations.net/IKOzVPjtHv3tevs-RDaJOMdtkBI/video/config.js
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/QwN0KdjTe-a-6y-70Vps9qMqCzM/gpt_and_prebid/config.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.64.144.166 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
66f1c1ed9421630251a28dc56a48a17da8acecd8eefa41aaf44baab0fd7d8c7a
Security Headers
Name Value
Strict-Transport-Security max-age=2592000

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
cf-cache-status
HIT
etag
"c5dcd8d7c24ee6ded8e122a656e397fd"
age
507
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
text/javascript
vary
accept-encoding
last-modified
Mon, 14 Sep 2026 01:32:50 GMT
priority
u=3,i=?0
x-amz-id-2
ZX7jFDWtsCV6p2pczkhjaGzS1byTEcBohH8CN9l/FfpGva0uWMmVR/Tom4MP93clvJzPc0lt7INzI1yXelaexkebou3QrxPC
strict-transport-security
max-age=2592000
cache-control
public, max-age=1100, stale-while-revalidate=3600
x-amz-request-id
KGZ6Q613Q4EHBAE9
cf-ray
a3abdc14dea237b0-AMS
accept-ranges
bytes
content-length
74570
server
cloudflare
x-amz-server-side-encryption
AES256
GET
H2
200
wf.js Show response
cdn.traffmovie.com/libs/
12 KB
12 KB
21ms
21ms
Script
application/javascript
178.162.196.143
LEASEWEB-DE-FRA-1...
General
Full URL
https://cdn.traffmovie.com/libs/wf.js
Requested by
Host: cdn.traffmovie.com
URL: https://cdn.traffmovie.com/libs/e.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
178.162.196.143 , Germany, ASN28753 (LEASEWEB-DE-FRA-10 Leaseweb Deutschland GmbH, DE),
Reverse DNS
Software
nginx /
Resource Hash
4b5587d97b275236a91526ee6ae980e45474af35956f86c242f30ccb4d618ce2
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block;

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
1728000
etag
"6a70b488-2e36"
access-control-allow-methods
GET, OPTIONS
x-content-type-options
nosniff
expires
Tue, 15 Sep 2026 02:11:12 GMT
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
application/javascript; charset=utf-8
last-modified
Mon, 03 Aug 2026 15:32:24 GMT
access-control-allow-headers
X-PINGOTHER
cache-control
max-age=86400
access-control-allow-credentials
true
accept-ranges
bytes
access-control-allow-origin
*
content-length
11830
x-xss-protection
1; mode=block;
server
nginx
GET
H2
204
load Show response
z.cdn.traffmovie.com/
0
195 B
56ms
14ms
Script
text/plain
95.211.37.134
LEASEWEB-NL-AMS-0...
General
Full URL
https://z.cdn.traffmovie.com/load?z=1650469738&div=zone_1650469738&cw=1600&ch=1200&sr=1600x1200&df=1&tz=120&bh=2&tl=2095&pl=5&mi=2&me=32&hc=30&n=1789351872790&v=true&i=true&scu=Chromium%3Bv%3D153%2C%20Google%20Chrome%3Bv%3D153%2C%20Not_A%20Brand%3Bv%3D8&scup=Linux&url=footyroom.co%2Fmatches%2F80034717%2Fmanchester-united-vs-sabah-fk%2Freview&vc=Intel%20Iris%20OpenGL%20Engine&ti=Manchester%20United%204-0%20Sabah%20FK%20Highlights%2C%20Goals%20%26%20Key%20Moments%20(10%20Sep%202026)%20%7C%20Champions%20League%20-%20Fo,football%2C%20soccer%2C%20highlights%2C%20statistics%2C%20goals%2C%20video,Watch%20Manchester%20United%204-0%20Sabah%20FK%20highlights%20and%20goals%20with%20key%20moments%2C%20stats%2C%20lineups%20and%20full%20&zyx=2842649399
Requested by
Host: cdn.traffmovie.com
URL: https://cdn.traffmovie.com/libs/e.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
95.211.37.134 , Netherlands, ASN60781 (LEASEWEB-NL-AMS-01 LeaseWeb Netherlands B.V., NL),
Reverse DNS
hosted-by.leaseweb.com
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

expires
-1
cache-control
no-cache, must-revalidate
date
Mon, 14 Sep 2026 02:11:12 GMT
pragma
no-cache
server
nginx
GET
H3
200
ads-arcspan.8fc7578a2d00f8aa7a18.js Show response
s.nitropay.com/
652 B
1 KB
25ms
25ms
Script
text/javascript
104.18.3.78
Cloudflare
General
Full URL
https://s.nitropay.com/ads-arcspan.8fc7578a2d00f8aa7a18.js
Requested by
Host: s.nitropay.com
URL: https://s.nitropay.com/ads-2321.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.18.3.78 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
6d51cc4c1338720545dc666f4df3fe1a78b2e9d97058dad6afe5c9353b60312c
Security Headers
Name Value
Strict-Transport-Security max-age=2592000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
access-control-expose-headers
Content-Type
x-goog-meta-goog-reserved-file-mtime
1789156610
x-goog-hash
crc32c=ANbcIA==, md5=y+Lz2NehjQkU3ES9FcDV3w==
cf-cache-status
HIT
etag
W/"cbe2f3d8d7a18d0914dc44bd15c0d5df"
age
193607
content-encoding
gzip
x-goog-stored-content-encoding
identity
expires
Sat, 11 Sep 2027 20:24:25 GMT
alt-svc
h3=":443"; ma=86400
x-goog-stored-content-length
652
server-timing
cfExtPri
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
text/javascript
last-modified
Fri, 11 Sep 2026 20:23:33 GMT
priority
u=3,i=?0
x-guploader-uploadid
AJjja9b0Mxm0vQ4zPv5CEXwu6QWJl7LONMZ3nsfOQxd0K5b18NYY6G7BSb4l0ax-yGIYX5wYX2sh7os
strict-transport-security
max-age=2592000; includeSubDomains
cache-control
public, max-age:43200
x-goog-storage-class
MULTI_REGIONAL
cf-ray
a3abdc150970fba3-AMS
access-control-allow-origin
*
x-goog-generation
1789158213789528
server
cloudflare
GET
H3
200
ads-captify.2015da149c7dcef90582.js Show response
s.nitropay.com/
892 B
1 KB
29ms
29ms
Script
text/javascript
104.18.3.78
Cloudflare
General
Full URL
https://s.nitropay.com/ads-captify.2015da149c7dcef90582.js
Requested by
Host: s.nitropay.com
URL: https://s.nitropay.com/ads-2321.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.18.3.78 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
eeaf94da90366254c9bd9e785dd8885dc14eb2802b41626208d111aea09c8fdb
Security Headers
Name Value
Strict-Transport-Security max-age=2592000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
access-control-expose-headers
Content-Type
x-goog-meta-goog-reserved-file-mtime
1789156610
x-goog-hash
crc32c=5Q7mFw==, md5=qEoSD+nn/C2U4j+VB8XYSA==
cf-cache-status
HIT
etag
W/"a84a120fe9e7fc2d94e23f9507c5d848"
age
193607
content-encoding
gzip
x-goog-stored-content-encoding
identity
expires
Sat, 11 Sep 2027 20:24:25 GMT
alt-svc
h3=":443"; ma=86400
x-goog-stored-content-length
892
server-timing
cfExtPri
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
text/javascript
last-modified
Fri, 11 Sep 2026 20:23:33 GMT
priority
u=3,i=?0
x-guploader-uploadid
AJjja9ZQuvkzQNU72-M1Q1636h7IoNYILwszv6nS775WKAdvhJa2FlyLNF9FZd6930dhpy2U25FLpUM
strict-transport-security
max-age=2592000; includeSubDomains
cache-control
public, max-age:43200
x-goog-storage-class
MULTI_REGIONAL
cf-ray
a3abdc150973fba3-AMS
access-control-allow-origin
*
x-goog-generation
1789158213857889
server
cloudflare
GET
H2
200
apstag.js Show response
c.amazon-adsystem.com/aax2/
365 KB
93 KB
81ms
24ms
Script
application/javascript
143.204.173.87
Amazon.com
General
Full URL
https://c.amazon-adsystem.com/aax2/apstag.js
Requested by
Host: s.nitropay.com
URL: https://s.nitropay.com/ads-2321.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
143.204.173.87 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-143-204-173-87.fra56.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
63fc76ea52a47bd52265c2e4cccc527ce2eac7576c34cd942c4a9ef310fc9009

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
cache-control
max-age=3600
content-encoding
gzip
etag
W/"9c74833dfe873db7cb801b766e20a2df"
age
3011
via
1.1 d63d8d406be99e2ae197739e9767d67e.cloudfront.net (CloudFront), 1.1 519a45a6eb7235ed934341d9b7a8cb2c.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
TIXHmDtucvce_uh7RN_5icMWq4YgkVXVqcRRap_vHzqycIg6sq8fdQ==
date
Mon, 14 Sep 2026 01:21:02 GMT
content-type
application/javascript
x-amz-cf-pop
FRA56-P14, FRA56-P17
server
AmazonS3
last-modified
Thu, 10 Sep 2026 19:53:04 GMT
x-amz-server-side-encryption
AES256
GET
H2
204
p
t.nit.ro/
0
0
501ms
456ms
Fetch
35.244.144.25
Google LLC
General
Full URL
https://t.nit.ro/p?d=QkpodHRwczovL2Zvb3R5cm9vbS5jby9tYXRjaGVzLzgwMDM0NzE3L21hbmNoZXN0ZXItdW5pdGVkLXZzLXNhYmFoLWZrL3Jldmlld1okMDFhMDlkYWUtYzkyNC03NTIzLWIxMTYtOTNiNjQ4MmY4MmJkYgJOTGoCTkiSASA4MDNhZTJkOTA1YmIxODNiYmFlZWIzNDUxODcyMzBiZJoBB2I1NjVjY2W4AQDQAZES2AEB
Requested by
Host: s.nitropay.com
URL: https://s.nitropay.com/ads-2321.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
35.244.144.25 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
25.144.244.35.bc.googleusercontent.com
Software
/
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

via
1.1 google
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:13 GMT
vary
Origin
GET
H3
200
ads-floating.a380b589c7f4f14cfbdb.js Show response
s.nitropay.com/
6 KB
3 KB
26ms
25ms
Script
text/javascript
104.18.3.78
Cloudflare
General
Full URL
https://s.nitropay.com/ads-floating.a380b589c7f4f14cfbdb.js
Requested by
Host: s.nitropay.com
URL: https://s.nitropay.com/ads-2321.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.18.3.78 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
1fa4bc01369d2d854e9fc64a454320682173fc228d05c0d5c5e088d15bdc3af1
Security Headers
Name Value
Strict-Transport-Security max-age=2592000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
access-control-expose-headers
Content-Type
x-goog-meta-goog-reserved-file-mtime
1789156610
x-goog-hash
crc32c=YAO8xw==, md5=OUsVEpOLSOI8dISmpU0iqQ==
cf-cache-status
HIT
etag
W/"394b1512938b48e23c7484a6a54d22a9"
age
193607
content-encoding
gzip
x-goog-stored-content-encoding
identity
expires
Sat, 11 Sep 2027 20:24:25 GMT
alt-svc
h3=":443"; ma=86400
x-goog-stored-content-length
5945
server-timing
cfExtPri
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
text/javascript
last-modified
Fri, 11 Sep 2026 20:23:34 GMT
priority
u=3,i=?0
x-guploader-uploadid
AJjja9brA69MZ3PTyUEwUPSPkmJ2uM5KvPPTnKIA7rNngUtHNGRx845st6TxdtDlNWVQ7zLjPdVQG0A
strict-transport-security
max-age=2592000; includeSubDomains
cache-control
public, max-age:43200
x-goog-storage-class
MULTI_REGIONAL
cf-ray
a3abdc1539c4fba3-AMS
access-control-allow-origin
*
x-goog-generation
1789158214113893
server
cloudflare
GET
H2
200
tag Show response
btloader.com/
155 KB
45 KB
76ms
33ms
Script
application/javascript
2606:4700:10::ac42:ab85
Cloudflare
General
Full URL
https://btloader.com/tag?o=6278260873756672&upapi=true
Requested by
Host: s.nitropay.com
URL: https://s.nitropay.com/ads-2321.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2606:4700:10::ac42:ab85 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
f4e2021ab2924dbb4a8604e09b90b0480dcb5d855df6f95ceb88cd0b6011e6ce

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-robots-tag
noindex, nofollow
cache-control
public, max-age=300, stale-if-error=3600, stale-while-revalidate=300
content-encoding
br
cf-cache-status
HIT
etag
W/"d6680e19b6ca34aceb3b5fe059f6acad"
via
1.1 google
cf-ray
a3abdc157bc36644-AMS
access-control-allow-origin
*
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
application/javascript
last-modified
Thu, 10 Sep 2026 15:55:10 GMT
server
cloudflare
vary
Accept-Encoding, X-Acceptable-Ads, DNT
GET
H2
200
/ Show response
geo.privacymanager.io/
30 B
429 B
78ms
23ms
Fetch
application/json
143.204.181.10
Amazon.com
General
Full URL
https://geo.privacymanager.io/
Requested by
Host: ats-wrapper.privacymanager.io
URL: https://ats-wrapper.privacymanager.io/ats-modules/438cb908-ed61-41e9-b716-05d5f4122a64/ats.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
143.204.181.10 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-143-204-181-10.fra56.r.cloudfront.net
Software
/
Resource Hash
3656ad0b9309abc5993e3cd41a5b83b18ae7e261fd007d16cb44d5e102520632

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-amz-apigw-id
Dqj1IEh9joEEk2Q=
age
2771
x-amzn-trace-id
Root=1-6aa74ced-5b1de2d425b5b4640b96d382;Parent=33368348cb9abac6;Sampled=0;Lineage=1:19b60b79:0
x-amzn-requestid
63c761b6-ba74-45ef-b7a3-bc49148c4a13
via
1.1 dacd42df730d14c2fb27b2bdb92f8196.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
content-length
30
x-amz-cf-id
RFIUh0QTTML_KIJZmfSAUr3_lkYi9bP1p7DUULv2lHMO8nwyv8sbew==
date
Mon, 14 Sep 2026 01:25:01 GMT
content-type
application/json
x-amz-cf-pop
FRA56-P17
GET
H3
200
pubads_impl.js Show response
securepubads.g.doubleclick.net/pagead/managed/js/gpt/m202609040101/
689 KB
212 KB
39ms
39ms
Script
text/javascript
142.251.127.156
Google LLC
General
Full URL
https://securepubads.g.doubleclick.net/pagead/managed/js/gpt/m202609040101/pubads_impl.js?cb=122880985
Requested by
Host: securepubads.g.doubleclick.net
URL: https://securepubads.g.doubleclick.net/tag/js/gpt.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.127.156 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfrai-in-f156.1e100.net
Software
cafe /
Resource Hash
37ec5817a0032426b8e9dd7991df9bc48d38d0b4ad358a8890dbe02fb92be13c
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://footyroom.co
sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
etag
11631903794125712047
age
52456
x-content-type-options
nosniff
expires
Mon, 13 Sep 2027 11:36:56 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
date
Sun, 13 Sep 2026 11:36:56 GMT
content-disposition
attachment; filename="f.txt"
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
cache-control
public, immutable, max-age=31536000
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
content-length
216949
x-xss-protection
0
server
cafe
POST
H2
200
collect Show response
www.google-analytics.com/j/
15 B
462 B
47ms
46ms
XHR
text/plain
2a00:1450:4001:c13::8a
Google LLC
General
Full URL
https://www.google-analytics.com/j/collect?v=1&_v=j102&a=637521320&t=pageview&_s=1&dl=https%3A%2F%2Ffootyroom.co%2Fmatches%2F80034717%2Fmanchester-united-vs-sabah-fk%2Freview&ul=nl-nl&dt=Manchester%20United%204-0%20Sabah%20FK%20Highlights%2C%20Goals%20%26%20Key%20Moments%20(10%20Sep%202026)%20%7C%20Champions%20League%20-%20FootyRoom&sr=1600x1200&vp=1600x1200&_u=YGBAAEABAAAAACAAI~&jid=1285955902&gjid=2064378335&cid=1302944229.1789351873&tid=UA-4779751-2&_gid=112525078.1789351873&_r=1&_slc=1&cd1=0&z=1095136624
Requested by
Host: www.google-analytics.com
URL: https://www.google-analytics.com/analytics.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a00:1450:4001:c13::8a Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
Golfe2 /
Resource Hash
60542d1c58f93ceb6dd83b360875978f07a0297d78989eef816778137f8c0159
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
text/plain
sec-ch-ua-mobile
?0

Response headers

report-to
{"group":"ascnsrsgac:207:0","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/scaffolding/ascnsrsgac:207:0"}],}
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:12 GMT
last-modified
Sun, 17 May 1998 03:00:00 GMT
content-type
text/plain
cache-control
no-cache, no-store, must-revalidate
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
content-security-policy-report-only
script-src 'none'; form-action 'none'; frame-src 'none'; report-uri https://csp.withgoogle.com/csp/scaffolding/ascnsrsgac:207:0
access-control-allow-origin
https://footyroom.co
cross-origin-opener-policy-report-only
same-origin; report-to=ascnsrsgac:207:0
content-length
15
server
Golfe2
GET
H3
200
id Show response
googleads.g.doubleclick.net/pagead/ Frame 6906
Redirect Chain
  • https://googleads.g.doubleclick.net/pagead/id
  • https://googleads.g.doubleclick.net/pagead/id?slf_rd=1
100 B
146 B
47ms
47ms
XHR
application/json
142.251.13.154
Google LLC
General
Full URL
https://googleads.g.doubleclick.net/pagead/id?slf_rd=1
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/ch_4efPW8xc?rel=0
Protocol
H3
Server
142.251.13.154 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
wt-in-f154.1e100.net
Software
cafe /
Resource Hash
7948dd3e7b6e12634b2eaa474d1caa8d6f86e54a095fd273838a8c2f335708ec
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer
https://www.youtube.com/

Response headers

content-encoding
gzip
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
application/json; charset=UTF-8
content-disposition
attachment; filename="f.txt"
cache-control
no-cache, no-store, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
access-control-allow-origin
https://www.youtube.com
content-length
120
x-xss-protection
0
server
cafe

Redirect headers

x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
text/html; charset=UTF-8
cache-control
no-cache, no-store, must-revalidate
location
https://googleads.g.doubleclick.net/pagead/id?slf_rd=1
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
access-control-allow-origin
https://www.youtube.com
content-length
0
x-xss-protection
0
server
cafe
GET
H2
200
ad_status.js Show response
static.doubleclick.net/instream/ Frame 6906
29 B
494 B
131ms
38ms
Script
text/javascript
2a00:1450:4001:c21::94
Google LLC
General
Full URL
https://static.doubleclick.net/instream/ad_status.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywHdVJjs6ktwWXG8Pg3CpN4ZEVjBaQ/m=root,base
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a00:1450:4001:c21::94 Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
eed0dc1fdb5d97ed188ae16fd5e1024a5bb744af47340346be2146300a6c54b9
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

age
83
report-to
{"group":"ads-doubleclick-media","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/ads-doubleclick-media"}]}
x-content-type-options
nosniff
expires
Mon, 14 Sep 2026 02:24:49 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:09:49 GMT
last-modified
Thu, 12 Dec 2013 23:40:16 GMT
content-type
text/javascript
cache-control
public, max-age=900
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to="ads-doubleclick-media"
content-length
29
x-xss-protection
0
server
sffe
GET
H3
200
m=r78Drb Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/ck=ytembeds.base.HY7wD9GGp-g.L.W.O/am=AAAAQA/d=1/exm=base,root/excm=base,root/ed=1/br=1/rs=AGKMywEii8DElVVeiaz1NP5LoXHZcDQ... Frame 6906
906 KB
219 KB
15ms
15ms
Script
text/javascript
142.251.150.4
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/ck=ytembeds.base.HY7wD9GGp-g.L.W.O/am=AAAAQA/d=1/exm=base,root/excm=base,root/ed=1/br=1/rs=AGKMywEii8DElVVeiaz1NP5LoXHZcDQCWg/m=r78Drb
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywHdVJjs6ktwWXG8Pg3CpN4ZEVjBaQ/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.150.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
86b742cfa596799c1a5856ba629afdd7b7b1e5478112bbb2101d126b9a2c75d9
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/ch_4efPW8xc?rel=0
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
220068
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Sat, 11 Sep 2027 13:03:24 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 11 Sep 2026 13:03:24 GMT
last-modified
Fri, 11 Sep 2026 03:12:40 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
223971
x-xss-protection
0
server
sffe
GET
H3
200
wlVpOs9ysPbT3guTARSwsoJIzHNbrijPiC3nWWfUumY.js Show response
www.google.com/js/th/ Frame 6906
62 KB
24 KB
30ms
14ms
Script
text/javascript
142.251.156.119
Google LLC
General
Full URL
https://www.google.com/js/th/wlVpOs9ysPbT3guTARSwsoJIzHNbrijPiC3nWWfUumY.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywHdVJjs6ktwWXG8Pg3CpN4ZEVjBaQ/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.156.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
c255693acf72b0f6d3de0b930114b0b28248cc735bae28cf882de75967d4ba66
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
455337
report-to
{"group":"botguard-scs","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/botguard-scs"}]}
x-content-type-options
nosniff
expires
Wed, 08 Sep 2027 19:42:15 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Tue, 08 Sep 2026 19:42:15 GMT
last-modified
Mon, 31 Aug 2026 16:00:00 GMT
content-type
text/javascript
vary
Accept-Encoding
cache-control
public, max-age=31536000
cross-origin-opener-policy
same-origin; report-to="botguard-scs"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/botguard-scs
accept-ranges
bytes
content-length
24304
x-xss-protection
0
server
sffe
GET
H2
200
js Show response
www.googletagmanager.com/gtag/
528 KB
176 KB
70ms
69ms
Script
application/javascript
2a00:1450:4001:c15::61
Google LLC
General
Full URL
https://www.googletagmanager.com/gtag/js?id=G-CGXL08N85B&cx=c&_slc=1
Requested by
Host: www.google-analytics.com
URL: https://www.google-analytics.com/analytics.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a00:1450:4001:c15::61 Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
Google Tag Manager /
Resource Hash
6d91bc6120d9947b8c5624f5e87fed0eb850c9140a2fe1c1bfc9987851431e79
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
private, max-age=900
content-encoding
zstd
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
expires
Mon, 14 Sep 2026 02:11:12 GMT
access-control-allow-origin
*
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
180106
date
Mon, 14 Sep 2026 02:11:12 GMT
x-xss-protection
0
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
server
Google Tag Manager
access-control-allow-headers
Cache-Control
GET
H3
200
in.php Show response
in.getclicky.com/
101 B
365 B
179ms
170ms
Fetch
text/javascript
104.16.225.240
Cloudflare
General
Full URL
https://in.getclicky.com/in.php?site_id=101475777&href=%2Fmatches%2F80034717%2Fmanchester-united-vs-sabah-fk%2Freview&title=Manchester%20United%204-0%20Sabah%20FK%20Highlights%2C%20Goals%20%26%20Key%20Moments%20(10%20Sep%202026)%20%7C%20Champions%20League%20-%20FootyRoom&res=1600x1200&lang=nl-NL&tz=Europe%2FAmsterdam&tc=&ck=1&x=1rpjws&f=1
Requested by
Host: static.getclicky.com
URL: https://static.getclicky.com/js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.16.225.240 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
0b7fb7d01e2b5aeddb1e38dc1ecc55635ba5c59efa8aba067925b6980ff91d1c

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-store, max-age=0
content-encoding
gzip
cf-cache-status
DYNAMIC
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
cf-ray
a3abdc15fbe9fe97-AMS
access-control-allow-origin
https://footyroom.co
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding, Accept-Encoding
server
cloudflare
priority
u=1,i
GET
H2
200
/
call.cleverwebserver.com/
43 B
105 B
53ms
40ms
Image
image/gif
2606:4700:4405::6812:21f7
Cloudflare
General
Full URL
https://call.cleverwebserver.com/?id=105375&c=NL&r=NH&l=219&b=Chrome&bv=0&os=Linux&mob=0&v=2.71.4&lg=nl-NL&ref=aHR0cHM6Ly9mb290eXJvb20uY28vbWF0Y2hlcy84MDAzNDcxNy9tYW5jaGVzdGVyLXVuaXRlZC12cy1zYWJhaC1may9yZXZpZXc%3D&ruri=&s=661d526acd138a565c8c2a8adcfce23c5948f6d4827445eac2bbfcdd3279d115&e=N7NCHuJW&st=W&iv=-1
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2606:4700:4405::6812:21f7 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
aa03dc59bdca72631d2301e4297cfa030bd31b907dc138e7b973d12311c90a22

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cf-ray
a3abdc160a8e285a-AMS
content-length
43
cf-cache-status
DYNAMIC
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
image/gif
server
cloudflare
GET
H2
200
/ Show response
geo.privacymanager.io/
30 B
427 B
21ms
21ms
Fetch
application/json
143.204.181.10
Amazon.com
General
Full URL
https://geo.privacymanager.io/
Requested by
Host: ats-wrapper.privacymanager.io
URL: https://ats-wrapper.privacymanager.io/ats-modules/438cb908-ed61-41e9-b716-05d5f4122a64/ats.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
143.204.181.10 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-143-204-181-10.fra56.r.cloudfront.net
Software
/
Resource Hash
3656ad0b9309abc5993e3cd41a5b83b18ae7e261fd007d16cb44d5e102520632

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-amz-apigw-id
Dqj1IEh9joEEk2Q=
age
2771
x-amzn-trace-id
Root=1-6aa74ced-5b1de2d425b5b4640b96d382;Parent=33368348cb9abac6;Sampled=0;Lineage=1:19b60b79:0
x-amzn-requestid
63c761b6-ba74-45ef-b7a3-bc49148c4a13
via
1.1 dacd42df730d14c2fb27b2bdb92f8196.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
content-length
30
x-amz-cf-id
ux47O2_LKYlXxXm4e4EKuJGKa33yeBgAsmA3UXFq1c5OMvqJn4nZww==
date
Mon, 14 Sep 2026 01:25:01 GMT
content-type
application/json
x-amz-cf-pop
FRA56-P17
GET
H3
200
m=cwx9N Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/ck=ytembeds.base.HY7wD9GGp-g.L.W.O/am=AAAAQA/d=1/exm=base,r78Drb,root/excm=base,root/ed=1/br=1/rs=AGKMywEii8DElVVeiaz1NP5L... Frame 6906
66 KB
17 KB
17ms
17ms
Script
text/javascript
142.251.156.119
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/ck=ytembeds.base.HY7wD9GGp-g.L.W.O/am=AAAAQA/d=1/exm=base,r78Drb,root/excm=base,root/ed=1/br=1/rs=AGKMywEii8DElVVeiaz1NP5LoXHZcDQCWg/m=cwx9N
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywHdVJjs6ktwWXG8Pg3CpN4ZEVjBaQ/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.156.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
9a6f174d593d8404d55c3ba5b8ddc199d63196b87c1cf40b061fe0266660af3d
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/ch_4efPW8xc?rel=0
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
220069
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Sat, 11 Sep 2027 13:03:24 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 11 Sep 2026 13:03:24 GMT
last-modified
Fri, 11 Sep 2026 03:12:40 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
17678
x-xss-protection
0
server
sffe
GET
H2
200
sddefault.webp
i.ytimg.com/vi_webp/ch_4efPW8xc/ Frame 6906
30 KB
30 KB
124ms
39ms
Image
image/webp
2a00:1450:4001:c17::77
Google LLC
General
Full URL
https://i.ytimg.com/vi_webp/ch_4efPW8xc/sddefault.webp
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/ch_4efPW8xc?rel=0
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a00:1450:4001:c17::77 Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
5299891a420281a888e79002f45eccaf4d9a78203d3eb47a5cce24122f38ff79
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

etag
"1789080398"
age
1210
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Mon, 14 Sep 2026 03:51:03 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 01:51:03 GMT
content-type
image/webp
vary
Origin
cache-control
public, max-age=7200
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
30472
x-xss-protection
0
server
sffe
GET
H2
200
OmFbKBxsMpaIN_20mhBGJwPP6mZEh6TXXbsTwG4633kXrGQMgV5WuvCfod8dGqBRBZzyfJzXeSc=s68-c-k-c0x00ffffff-no-rj
yt3.ggpht.com/ Frame 6906
4 KB
5 KB
130ms
39ms
Image
image/jpeg
2a00:1450:4001:c13::84
Google LLC
General
Full URL
https://yt3.ggpht.com/OmFbKBxsMpaIN_20mhBGJwPP6mZEh6TXXbsTwG4633kXrGQMgV5WuvCfod8dGqBRBZzyfJzXeSc=s68-c-k-c0x00ffffff-no-rj
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/ch_4efPW8xc?rel=0
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a00:1450:4001:c13::84 Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
fife /
Resource Hash
61423dca26858bc9c29ff972df1cf3207de529f3c8892577fb01713d200d2b42
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

access-control-expose-headers
Content-Length
etag
"v1"
age
253
x-content-type-options
nosniff
expires
Tue, 15 Sep 2026 02:07:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:07:00 GMT
content-disposition
inline;filename="channels4_profile.jpg"
content-type
image/jpeg
vary
Origin
cache-control
public, max-age=86400, no-transform
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
content-length
4315
x-xss-protection
0
server
fife
GET
H2
200
67px.svg Show response
www.gstatic.com/youtube/img/icons/mweb/youtube_fill/logo/v2/ Frame 6906
478 B
725 B
131ms
41ms
Fetch
image/svg+xml
2a00:1450:4001:c17::5e
Google LLC
General
Full URL
https://www.gstatic.com/youtube/img/icons/mweb/youtube_fill/logo/v2/67px.svg
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/ck=ytembeds.base.HY7wD9GGp-g.L.W.O/am=AAAAQA/d=1/exm=base,root/excm=base,root/ed=1/br=1/rs=AGKMywEii8DElVVeiaz1NP5LoXHZcDQCWg/m=r78Drb
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a00:1450:4001:c17::5e Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
6fa88a20839537ae66da730e5bd183035265176d972bc8df075b89da0c6186ea
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
681
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Tue, 14 Sep 2027 01:59:52 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 01:59:52 GMT
last-modified
Wed, 06 Sep 2023 03:18:00 GMT
content-type
image/svg+xml
vary
Accept-Encoding, Origin
cache-control
public, max-age=31536000
cross-origin-opener-policy
same-origin; report-to="youtube"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
https://www.youtube.com
content-length
272
x-xss-protection
0
server
sffe
GET
H2
200
as1.js Show response
silo60.p7cloud.net/
792 KB
169 KB
98ms
24ms
Script
application/javascript
2600:9000:26e8:a200:11:a9de:ec0:93a1
Amazon.com
General
Full URL
https://silo60.p7cloud.net/as1.js?uri=https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Requested by
Host: s.nitropay.com
URL: https://s.nitropay.com/ads-2321.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2600:9000:26e8:a200:11:a9de:ec0:93a1 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
Software
AmazonS3 /
Resource Hash
c479d6783f4479d3d6c4f205ff2c31b8c915cae131d7c892672cb3cb6f266803

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-amz-cf-pop
FRA56-P10
content-encoding
gzip
etag
W/"903d514fbecc45c911c017cf824c56ac"
age
57942
via
1.1 adffa554e502bb59dc89f14ddc6170ce.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
cLdFZ-GVIedc52IfTWZxtxy1OVqKa-QQUV6d1GItdTqzKBLBhCdITw==
date
Sun, 13 Sep 2026 10:05:32 GMT
content-type
application/javascript
vary
Accept-Encoding
server
AmazonS3
last-modified
Fri, 11 Sep 2026 11:16:21 GMT
x-amz-server-side-encryption
AES256
GET
H3
200
wrap.js Show response
cdn.confiant-integrations.net/video/202609031720/
363 KB
127 KB
19ms
19ms
Script
application/javascript
172.64.144.166
Cloudflare
General
Full URL
https://cdn.confiant-integrations.net/video/202609031720/wrap.js
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/IKOzVPjtHv3tevs-RDaJOMdtkBI/video/config.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.64.144.166 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
c224df7cafde922452b0f7dddd8e6459faffee48b19cb46ce2d0d0242ca053a9
Security Headers
Name Value
Strict-Transport-Security max-age=2592000

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
cf-cache-status
HIT
etag
"9f1e0d9a0302496bf131e103a1e73ab3"
age
463669
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
application/javascript; charset=utf-8
vary
accept-encoding
last-modified
Thu, 03 Sep 2026 14:23:59 GMT
priority
u=3,i=?0
x-amz-id-2
vh1YzmprWmXuccI5LgWWNc/5SS7+07nioF30iVaX/Xmqzh57IV156IReCssUn5xYuVQxN3tEhUeTbxmMfrDOhwccz5BmoBhL
strict-transport-security
max-age=2592000
cache-control
public, max-age=31536000
x-amz-request-id
03MER5GDMF0DYPWF
cf-ray
a3abdc16eada37b0-AMS
accept-ranges
bytes
content-length
129385
server
cloudflare
x-amz-server-side-encryption
AES256
GET
H3
204
generate_204
www.youtube.com/ Frame 6906
0
10 B
14ms
14ms
Image
text/plain
142.251.156.119
Google LLC
General
Full URL
https://www.youtube.com/generate_204?ZaJJwg
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/ch_4efPW8xc?rel=0
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.156.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/ch_4efPW8xc?rel=0
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
0
date
Mon, 14 Sep 2026 02:11:13 GMT
cross-origin-resource-policy
cross-origin
GET
BLOB
200
OK
f9962497-5425-4f42-889f-0acd9e99c7b5 Show response
https://footyroom.co/ Frame D46F
4 KB
0
Script
application/javascript

General
Full URL
blob:https://footyroom.co/f9962497-5425-4f42-889f-0acd9e99c7b5
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
BLOB
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
c393667527928f97793fc1ae916eeb5bb53ebfbf475acca4d7f7858a84f2807b

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
application/javascript
Content-Length
4438
OPTIONS
H2
200
GenerateIT
jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/ Frame
0
0
59ms
19ms
Preflight
text/html
2001:4860:4845:400::
Google LLC
General
Full URL
https://jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/GenerateIT
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2001:4860:4845:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

Accept
*/*
Access-Control-Request-Headers
content-type,x-goog-api-key
Access-Control-Request-Method
POST
Origin
https://www.youtube.com
Sec-Fetch-Mode
cors
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36

Response headers

access-control-allow-credentials
true
access-control-allow-headers
content-type,x-goog-api-key
access-control-allow-methods
DELETE,GET,HEAD,OPTIONS,PATCH,POST,PUT
access-control-allow-origin
https://www.youtube.com
access-control-max-age
3600
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
0
content-type
text/html
date
Mon, 14 Sep 2026 02:11:13 GMT
server
ESF
vary
origin referer x-origin
x-content-type-options
nosniff
x-frame-options
SAMEORIGIN
x-xss-protection
0
POST
H2
200
GenerateIT Show response
jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/ Frame 6906
94 B
304 B
25ms
23ms
XHR
application/json+protobuf
2001:4860:4845:400::
Google LLC
General
Full URL
https://jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/GenerateIT
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywHdVJjs6ktwWXG8Pg3CpN4ZEVjBaQ/m=root,base
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2001:4860:4845:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
1e6a48f545fe9a849b2e085519ede5fdf1893b4b273b73f3ba7ce0df22397277
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

X-Goog-Api-Key
AIzaSyDyT5W0Jh49F30Pqqtyfdf7pDLFKLJoAnw
sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
application/json+protobuf
sec-ch-ua-mobile
?0

Response headers

access-control-expose-headers
vary,vary,vary,content-encoding,date,server,content-length
content-encoding
gzip
access-control-allow-credentials
true
x-content-type-options
nosniff
access-control-allow-origin
https://www.youtube.com
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
114
date
Mon, 14 Sep 2026 02:11:13 GMT
x-xss-protection
0
content-type
application/json+protobuf; charset=UTF-8
vary
Origin, X-Origin, Referer
server
ESF
x-frame-options
SAMEORIGIN
GET
H3
200
ads-floating.d67d22508ef41ecbe965.css
s.nitropay.com/
1 KB
972 B
26ms
25ms
Stylesheet
text/css
104.18.3.78
Cloudflare
General
Full URL
https://s.nitropay.com/ads-floating.d67d22508ef41ecbe965.css
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.18.3.78 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
3a16b6fe0a26fecd8d0bfb084c415b3981f3ba2046ac0983d1c3b1b2859be26c
Security Headers
Name Value
Strict-Transport-Security max-age=2592000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
access-control-expose-headers
Content-Type
x-goog-meta-goog-reserved-file-mtime
1789077838
x-goog-hash
crc32c=bdpLPQ==, md5=2QMf8q9s7S1zDXZGP38m7g==
cf-cache-status
HIT
etag
W/"d9031ff2af6ced2d730d76463f7f26ee"
age
193606
content-encoding
gzip
x-goog-stored-content-encoding
identity
expires
Sat, 11 Sep 2027 20:24:26 GMT
alt-svc
h3=":443"; ma=86400
x-goog-stored-content-length
1149
server-timing
cfExtPri
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
text/css
last-modified
Fri, 11 Sep 2026 20:23:33 GMT
priority
u=0,i=?0
x-guploader-uploadid
AJjja9bIlWzEAkI5jNiJ1vAzEK8UoUOd8mbDR1EQ8io_LZsyZEV85N280sDYBtYJ8TW_t5Tv
strict-transport-security
max-age=2592000; includeSubDomains
cache-control
public, max-age:43200
x-goog-storage-class
MULTI_REGIONAL
cf-ray
a3abdc17aea3fba3-AMS
access-control-allow-origin
*
x-goog-generation
1789077886857367
server
cloudflare
GET
H2
200
cchecker.html Show response
cdn.btloader.com/ Frame FD0E
366 B
774 B
58ms
19ms
Document
text/html
2606:4700:10::ac42:ab85
Cloudflare
General
Full URL
https://cdn.btloader.com/cchecker.html?upapi=true
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2606:4700:10::ac42:ab85 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
c700c58e763a5ae34f446713819957ed9755025d35b8497ec1150f428f5ff227

Request headers

Referer
https://footyroom.co/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

access-control-allow-origin
*
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
age
295934
cache-control
public, max-age=86400, immutable
cf-cache-status
HIT
cf-ray
a3abdc180bf6f18a-AMS
content-encoding
br
content-type
text/html
date
Mon, 14 Sep 2026 02:11:13 GMT
expires
Fri, 11 Sep 2026 15:50:14 GMT
last-modified
Thu, 16 Apr 2026 14:02:40 GMT
server
cloudflare
x-goog-generation
1776348160499015
x-goog-hash
crc32c=/3eT+A== md5=WtMW8Jy4XJceDGzQqhOktA==
x-goog-metageneration
1
x-goog-storage-class
MULTI_REGIONAL
x-goog-stored-content-encoding
identity
x-goog-stored-content-length
366
x-guploader-uploadid
AJjja9YOBcHjjq1C33hn6IxNWvn6CrPxWv1jaNZQLayruqoqAouRyp2Pa1Q1jVyZ5nGXjFVi
GET
H2
200
px.gif Show response
ad-delivery.net/
43 B
109 B
62ms
23ms
Fetch
image/gif
2606:4700:10::ac42:948c
Cloudflare
General
Full URL
https://ad-delivery.net/px.gif?ch=2&e=0.23089392416774102
Requested by
Host: btloader.com
URL: https://btloader.com/tag?o=6278260873756672&upapi=true
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2606:4700:10::ac42:948c -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
cf4724b2f736ed1a0ae6bc28f1ead963d9cd2c1fd87b6ef32e7799fc1c5c8bda

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
5
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=cpEfJQ==, md5=rUsPYG4PhGW8TEwXCzfhow==
cf-cache-status
HIT
etag
"ad4b0f606e0f8465bc4c4c170b37e1a3"
age
2223
x-goog-stored-content-encoding
identity
expires
Mon, 14 Sep 2026 01:56:21 GMT
x-goog-stored-content-length
43
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
image/gif
last-modified
Wed, 05 May 2021 19:25:32 GMT
x-guploader-uploadid
AKhXX7Ij0HsF82F-154UYfFX1Gp5cCmGjgS1xTm34ZQjp8FSns2hC9fd1cFeCxd11HNskCSYP4DIRTI
cache-control
public, max-age=86400
x-goog-storage-class
MULTI_REGIONAL
cf-ray
a3abdc180ad98b7c-AMS
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1620242732037093
content-length
43
server
cloudflare
GET
H3
200
favicon.ico Show response
ad.doubleclick.net/
1 KB
129 B
102ms
48ms
Fetch
image/x-icon
142.251.14.149
Google LLC
General
Full URL
https://ad.doubleclick.net/favicon.ico?ad=300x250&ad_box_=1&adnet=1&showad=1&size=250x250&e=0.36715247391567873
Requested by
Host: btloader.com
URL: https://btloader.com/tag?o=6278260873756672&upapi=true
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.14.149 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f149.1e100.net
Software
sffe /
Resource Hash
d961b08e4321250926de6f79087594975fe20ad1518de8f91eb711af5d1a6ef8
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
report-to
{"group":"ads-doubleclick-media","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/ads-doubleclick-media"}]}
x-content-type-options
nosniff
expires
Tue, 15 Sep 2026 02:11:13 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
image/x-icon
vary
Accept-Encoding
last-modified
Tue, 08 May 2012 13:08:06 GMT
cache-control
public, max-age=86400
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to="ads-doubleclick-media"
content-length
104
x-xss-protection
0
server
sffe
GET
H2
200
px.gif Show response
ad-delivery.net/
43 B
613 B
58ms
20ms
Fetch
image/gif
2606:4700:10::ac42:948c
Cloudflare
General
Full URL
https://ad-delivery.net/px.gif?ch=1&e=0.7510398880906368
Requested by
Host: btloader.com
URL: https://btloader.com/tag?o=6278260873756672&upapi=true
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2606:4700:10::ac42:948c -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
cf4724b2f736ed1a0ae6bc28f1ead963d9cd2c1fd87b6ef32e7799fc1c5c8bda

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
5
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=cpEfJQ==, md5=rUsPYG4PhGW8TEwXCzfhow==
cf-cache-status
HIT
etag
"ad4b0f606e0f8465bc4c4c170b37e1a3"
age
2223
x-goog-stored-content-encoding
identity
expires
Mon, 14 Sep 2026 01:56:21 GMT
x-goog-stored-content-length
43
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
image/gif
last-modified
Wed, 05 May 2021 19:25:32 GMT
x-guploader-uploadid
AKhXX7Ij0HsF82F-154UYfFX1Gp5cCmGjgS1xTm34ZQjp8FSns2hC9fd1cFeCxd11HNskCSYP4DIRTI
cache-control
public, max-age=86400
x-goog-storage-class
MULTI_REGIONAL
cf-ray
a3abdc180acd8b7c-AMS
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1620242732037093
content-length
43
server
cloudflare
GET
H2
200
dns Show response
ab.dns-finder.com/meta/
2 B
233 B
513ms
448ms
Fetch
text/plain
34.36.200.111
Google LLC
General
Full URL
https://ab.dns-finder.com/meta/dns
Requested by
Host: btloader.com
URL: https://btloader.com/tag?o=6278260873756672&upapi=true
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.36.200.111 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
111.200.36.34.bc.googleusercontent.com
Software
/
Resource Hash
2689367b205c16ce32ed4200942b8b8b1e262dfc70d9bc9fbc77c49699a4f1df

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
private, max-age=180, stale-if-error=180, stale-while-revalidate=180
access-control-expose-headers
X-Resolver
x-resolver
default
via
1.1 google
access-control-allow-origin
*
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
2
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
text/plain; charset=utf-8
vary
Origin
GET
H2
200
trustedIframe.html Show response
btloader.com/ Frame B49C
6 KB
2 KB
58ms
29ms
Document
text/html
2606:4700:10::6814:14bd
Cloudflare
General
Full URL
https://btloader.com/trustedIframe.html?o=6278260873756672&upapi=true
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2606:4700:10::6814:14bd -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
36b4cda222f74c9ceaebf5b2dfca34066f00f0eb139c4904247de0aa869a0d69

Request headers

Referer
https://footyroom.co/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

cache-control
public, max-age=3600, stale-while-revalidate=3600
cf-ray
a3abdc17fada7875-AMS
content-encoding
br
content-type
text/html
date
Mon, 14 Sep 2026 02:11:13 GMT
server
cloudflare
GET
H2
403
device Show response
cdn.api.btloader.com/
1 B
237 B
87ms
45ms
Fetch
text/plain
2606:4700:10::ac42:ab85
Cloudflare
General
Full URL
https://cdn.api.btloader.com/device?orgid=6278260873756672&fullVersionList=%5B%7B%22brand%22%3A%22Chromium%22%2C%22version%22%3A%22153.0.0.0%22%7D%2C%7B%22brand%22%3A%22Google+Chrome%22%2C%22version%22%3A%22153.0.0.0%22%7D%2C%7B%22brand%22%3A%22Not_A+Brand%22%2C%22version%22%3A%228.0.0.0%22%7D%5D&upapi=true
Requested by
Host: btloader.com
URL: https://btloader.com/tag?o=6278260873756672&upapi=true
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2606:4700:10::ac42:ab85 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
01ba4719c80b6fe911b091a7c05124b64eeece964e09c058ef8f9805daca546b
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cf-cache-status
DYNAMIC
x-ratelimit-reset
1789351874
x-content-type-options
nosniff
via
1.1 google
cf-ray
a3abdc181b38671f-AMS
x-ratelimit-remaining
99
access-control-allow-origin
*
content-length
1
date
Mon, 14 Sep 2026 02:11:13 GMT
x-ratelimit-limit
100
content-type
text/plain; charset=utf-8
vary
Origin
server
cloudflare
GET
H2
200
da657530-03e5-4306-95bc-d4eb370426c9 Show response
config.aps.amazon-adsystem.com/configs/
10 KB
2 KB
78ms
22ms
Script
application/javascript
18.245.31.123
Amazon.com
General
Full URL
https://config.aps.amazon-adsystem.com/configs/da657530-03e5-4306-95bc-d4eb370426c9
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
18.245.31.123 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-18-245-31-123.fra56.r.cloudfront.net
Software
CloudFront /
Resource Hash
21708fe6f20640f454dc6792440b20ebd67fba3a60b36c2a7267e30b651e9df0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=3600
content-encoding
gzip
age
708
via
1.1 a530f843a2269d63579bc4238b63fbac.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
content-length
2123
x-amz-cf-id
Y9QFJiGiqfGlpSwa30koJUFB4wuoRvQMvjhla-exI-LrA7G_0_QgCw==
date
Mon, 14 Sep 2026 01:59:25 GMT
content-type
application/javascript
x-amz-cf-pop
FRA56-P8
server
CloudFront
GET
H2
200
aps_csm.js Show response
c.amazon-adsystem.com/bao-csm/aps-comm/
6 KB
3 KB
64ms
21ms
XHR
application/javascript
143.204.173.87
Amazon.com
General
Full URL
https://c.amazon-adsystem.com/bao-csm/aps-comm/aps_csm.js
Requested by
Host: c.amazon-adsystem.com
URL: https://c.amazon-adsystem.com/aax2/apstag.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
143.204.173.87 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-143-204-173-87.fra56.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
06b99248a163333e36980a6cfb756f1a7de60fa49517162b87b1a44d5d48f844

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
3000
content-encoding
gzip
x-amz-version-id
r5.lR.LJ66XEXzxUUVo7iMemjL_F_GoE
etag
W/"a4d296427fc806b21335359e398c025c"
age
84175
access-control-allow-methods
GET
x-cache
Hit from cloudfront
x-amz-cf-id
GzD2qc5Rzimlc-1NsxBnwomQczmJiYvSIvDLhYT9jAL85XNcIAca2Q==
date
Sun, 13 Sep 2026 02:48:19 GMT
content-type
application/javascript
vary
Origin,Accept-Encoding
last-modified
Thu, 29 Feb 2024 02:13:08 GMT
cache-control
public, max-age=86400
via
1.1 5d1fa985bc0f71542b20316391cdb282.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-amz-cf-pop
FRA56-P17
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H2
200
adunit Show response
srv.scalibur.io/adserver/ Frame 9E78
310 KB
86 KB
42ms
42ms
Script
text/javascript
185.167.98.14
CloudWebManage-EU...
General
Full URL
https://srv.scalibur.io/adserver/adunit?id=56&width=970&height=90&url=https%3A%2F%2Ffootyroom.co%2Fmatches%2F80034717%2Fmanchester-united-vs-sabah-fk%2Freview&sids=%7B%7D&schain=1.0%2C1!nitropay.com%2C1728%2C1%2C%2C%2C&containerId=Match%20Highlights-isolated&isDebug=0&cb=1789351873336_kzlsm4&us_privacy=1---&keyValues=%7B%22gamAdUnitId%22%3A%22%2F308365556%2C22913055933%2Fnitro-banner%2Fnitro-banner-2321%22%2C%22ttdPubId%22%3A%221728%22%2C%22siteId%22%3A%222321%22%2C%22nitro_gpid%22%3A%22Match%20Highlights%22%7D
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
185.167.98.14 Amsterdam, Netherlands, ASN41436 (CloudWebManage-EU Kamatera Inc, US),
Reverse DNS
Software
/
Resource Hash
7f11fe296be962098dd3f887faf2a349c44b45761732dd016936f31f3cfdcace
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
no-store
content-encoding
gzip
pragma
no-cache
age
0
expires
0
access-control-allow-origin
*
content-length
87836
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
text/javascript; charset=UTF-8
GET
H2
200
adunit Show response
srv.scalibur.io/adserver/ Frame 14B4
337 KB
88 KB
66ms
66ms
Script
text/javascript
185.167.98.14
CloudWebManage-EU...
General
Full URL
https://srv.scalibur.io/adserver/adunit?id=56&width=300&height=169&url=https%3A%2F%2Ffootyroom.co%2Fmatches%2F80034717%2Fmanchester-united-vs-sabah-fk%2Freview&sids=%7B%7D&schain=1.0%2C1!nitropay.com%2C1728%2C1%2C%2C%2C&containerId=Nitro%20Desktop%20Video%20Ad-isolated&isDebug=0&cb=1789351873339_1cdfuw&us_privacy=1---&keyValues=%7B%22gamAdUnitId%22%3A%22%2F308365556%2C22913055933%2Fnitro-banner%2Fnitro-banner-2321%22%2C%22ttdPubId%22%3A%221728%22%2C%22siteId%22%3A%222321%22%2C%22nitro_gpid%22%3A%22Nitro%20Desktop%20Video%20Ad%22%7D
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
185.167.98.14 Amsterdam, Netherlands, ASN41436 (CloudWebManage-EU Kamatera Inc, US),
Reverse DNS
Software
/
Resource Hash
65c58dc713ec4def44139bd459f870adbf29a0a86bf74775a2ed33658441274f
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
no-store
content-encoding
gzip
pragma
no-cache
age
0
expires
0
access-control-allow-origin
*
content-length
89982
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
text/javascript; charset=UTF-8
GET
H2
200
grumi-ip.js Show response
rumcdn.geoedge.be/3c5f792e-2099-4b89-b2fa-171ced5152e0/ Frame 9E78
18 KB
7 KB
94ms
22ms
Script
application/javascript
2600:9000:2013:ac00:4:b37b:9440:93a1
Amazon.com
General
Full URL
https://rumcdn.geoedge.be/3c5f792e-2099-4b89-b2fa-171ced5152e0/grumi-ip.js
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2600:9000:2013:ac00:4:b37b:9440:93a1 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
Software
AmazonS3 /
Resource Hash
dd10579531923f3143b13c06cc3aaadf7af3d9df1c20eb83dc50e7b63518758f

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
cache-control
public, max-age=14400, stale-while-revalidate=14400, immutable
content-encoding
br
x-amz-version-id
KPNMOg2qpW7KGY5K2zkNUfZMWrRtw21d
etag
W/"30fea97d0d7ea56d1cdd9c60ab709dc0"
age
1260
via
1.1 e4a99a83f5512cdd81d7e04f709bb800.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
OXNBRgWGcTs5PTdR1NvbbF_lUCFLksUrGsp6re_2gc9prNEzobp19Q==
date
Mon, 14 Sep 2026 01:50:14 GMT
content-type
application/javascript
last-modified
Tue, 01 Sep 2026 12:58:20 GMT
server
AmazonS3
x-amz-cf-pop
FRA56-P14
x-amz-server-side-encryption
AES256
GET
H2
200
prebid9.53.3-new.js Show response
srv.scalibur.io/adserver/static/ Frame 22B1
529 KB
178 KB
42ms
41ms
Script
text/javascript
185.167.98.14
CloudWebManage-EU...
General
Full URL
https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/adunit?id=56&width=970&height=90&url=https%3A%2F%2Ffootyroom.co%2Fmatches%2F80034717%2Fmanchester-united-vs-sabah-fk%2Freview&sids=%7B%7D&schain=1.0%2C1!nitropay.com%2C1728%2C1%2C%2C%2C&containerId=Match%20Highlights-isolated&isDebug=0&cb=1789351873336_kzlsm4&us_privacy=1---&keyValues=%7B%22gamAdUnitId%22%3A%22%2F308365556%2C22913055933%2Fnitro-banner%2Fnitro-banner-2321%22%2C%22ttdPubId%22%3A%221728%22%2C%22siteId%22%3A%222321%22%2C%22nitro_gpid%22%3A%22Match%20Highlights%22%7D
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
185.167.98.14 Amsterdam, Netherlands, ASN41436 (CloudWebManage-EU Kamatera Inc, US),
Reverse DNS
Software
/
Resource Hash
6a5d3217bae4baa9358b0bddfc3b305154aa34fecb52735e3652c3096f3eb899
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
no-cache, no-store, must-revalidate
content-encoding
gzip
pragma
no-cache
age
0
expires
0
access-control-allow-origin
*
content-length
182253
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
text/javascript
GET
H2
200
ima3.js Show response
imasdk.googleapis.com/js/sdkloader/ Frame 9E78
502 KB
155 KB
172ms
78ms
Script
text/javascript
2a00:1450:4001:c15::5f
Google LLC
General
Full URL
https://imasdk.googleapis.com/js/sdkloader/ima3.js
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a00:1450:4001:c15::5f Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
cafe /
Resource Hash
b69ef083bc12058a1b5cf6e59d261c3914e079869a3c126ac134ec4e119509f5
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
etag
14570173725857091252
x-content-type-options
nosniff
expires
Mon, 14 Sep 2026 02:11:13 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-disposition
attachment; filename="f.txt"
cache-control
private, max-age=900, stale-while-revalidate=3600
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
content-length
157877
x-xss-protection
0
server
cafe
GET
H3
200
gpt.js Show response
securepubads.g.doubleclick.net/tag/js/ Frame 9E78
125 KB
0
109ms
109ms
Script
text/javascript
142.251.127.156
Google LLC
General
Full URL
https://securepubads.g.doubleclick.net/tag/js/gpt.js
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.127.156 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfrai-in-f156.1e100.net
Software
cafe /
Resource Hash
fb5290615c75705d27dded2a331aac90e6c5eabba48941bbd78b52c3af158975
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://footyroom.co/

Response headers

content-encoding
br
etag
128 / 20710 / 122880985 / config-hash: 17945051965659213301
x-content-type-options
nosniff
expires
Mon, 14 Sep 2026 02:11:12 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-disposition
attachment; filename="f.txt"
cache-control
private, max-age=900, stale-while-revalidate=3600
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
content-length
38384
x-xss-protection
0
server
cafe
GET
H2
200
grumi-ip.js Show response
rumcdn.geoedge.be/3c5f792e-2099-4b89-b2fa-171ced5152e0/ Frame 14B4
18 KB
0
89ms
89ms
Script
application/javascript
2600:9000:2013:ac00:4:b37b:9440:93a1
Amazon.com
General
Full URL
https://rumcdn.geoedge.be/3c5f792e-2099-4b89-b2fa-171ced5152e0/grumi-ip.js
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2600:9000:2013:ac00:4:b37b:9440:93a1 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
Software
AmazonS3 /
Resource Hash
dd10579531923f3143b13c06cc3aaadf7af3d9df1c20eb83dc50e7b63518758f

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
cache-control
public, max-age=14400, stale-while-revalidate=14400, immutable
content-encoding
br
x-amz-version-id
KPNMOg2qpW7KGY5K2zkNUfZMWrRtw21d
etag
W/"30fea97d0d7ea56d1cdd9c60ab709dc0"
age
1260
via
1.1 e4a99a83f5512cdd81d7e04f709bb800.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
OXNBRgWGcTs5PTdR1NvbbF_lUCFLksUrGsp6re_2gc9prNEzobp19Q==
date
Mon, 14 Sep 2026 01:50:14 GMT
content-type
application/javascript
last-modified
Tue, 01 Sep 2026 12:58:20 GMT
server
AmazonS3
x-amz-cf-pop
FRA56-P14
x-amz-server-side-encryption
AES256
GET
H2
200
prebid9.53.3-new.js Show response
srv.scalibur.io/adserver/static/ Frame A4C8
529 KB
178 KB
80ms
42ms
Script
text/javascript
185.167.98.14
CloudWebManage-EU...
General
Full URL
https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/adunit?id=56&width=300&height=169&url=https%3A%2F%2Ffootyroom.co%2Fmatches%2F80034717%2Fmanchester-united-vs-sabah-fk%2Freview&sids=%7B%7D&schain=1.0%2C1!nitropay.com%2C1728%2C1%2C%2C%2C&containerId=Nitro%20Desktop%20Video%20Ad-isolated&isDebug=0&cb=1789351873339_1cdfuw&us_privacy=1---&keyValues=%7B%22gamAdUnitId%22%3A%22%2F308365556%2C22913055933%2Fnitro-banner%2Fnitro-banner-2321%22%2C%22ttdPubId%22%3A%221728%22%2C%22siteId%22%3A%222321%22%2C%22nitro_gpid%22%3A%22Nitro%20Desktop%20Video%20Ad%22%7D
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
185.167.98.14 Amsterdam, Netherlands, ASN41436 (CloudWebManage-EU Kamatera Inc, US),
Reverse DNS
Software
/
Resource Hash
6a5d3217bae4baa9358b0bddfc3b305154aa34fecb52735e3652c3096f3eb899
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
no-cache, no-store, must-revalidate
content-encoding
gzip
pragma
no-cache
age
0
expires
0
access-control-allow-origin
*
content-length
182253
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
text/javascript
GET
H2
200
ima3.js Show response
imasdk.googleapis.com/js/sdkloader/ Frame 14B4
502 KB
0
168ms
168ms
Script
text/javascript
2a00:1450:4001:c15::5f
Google LLC
General
Full URL
https://imasdk.googleapis.com/js/sdkloader/ima3.js
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a00:1450:4001:c15::5f Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
cafe /
Resource Hash
b69ef083bc12058a1b5cf6e59d261c3914e079869a3c126ac134ec4e119509f5
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
etag
14570173725857091252
x-content-type-options
nosniff
expires
Mon, 14 Sep 2026 02:11:13 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-disposition
attachment; filename="f.txt"
cache-control
private, max-age=900, stale-while-revalidate=3600
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
content-length
157877
x-xss-protection
0
server
cafe
GET
H3
200
gpt.js Show response
securepubads.g.doubleclick.net/tag/js/ Frame 14B4
125 KB
0
109ms
109ms
Script
text/javascript
142.251.127.156
Google LLC
General
Full URL
https://securepubads.g.doubleclick.net/tag/js/gpt.js
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.127.156 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfrai-in-f156.1e100.net
Software
cafe /
Resource Hash
fb5290615c75705d27dded2a331aac90e6c5eabba48941bbd78b52c3af158975
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://footyroom.co/

Response headers

content-encoding
br
etag
128 / 20710 / 122880985 / config-hash: 17945051965659213301
x-content-type-options
nosniff
expires
Mon, 14 Sep 2026 02:11:12 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
date
Mon, 14 Sep 2026 02:11:12 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-disposition
attachment; filename="f.txt"
cache-control
private, max-age=900, stale-while-revalidate=3600
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
content-length
38384
x-xss-protection
0
server
cafe
GET
H3
200
pubads_impl.js Show response
securepubads.g.doubleclick.net/pagead/managed/js/gpt/m202609040101/ Frame 9E78
689 KB
0
0ms
0ms
Script
text/javascript
142.251.127.156
Google LLC
General
Full URL
https://securepubads.g.doubleclick.net/pagead/managed/js/gpt/m202609040101/pubads_impl.js?cb=122880985
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.127.156 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfrai-in-f156.1e100.net
Software
cafe /
Resource Hash
37ec5817a0032426b8e9dd7991df9bc48d38d0b4ad358a8890dbe02fb92be13c
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
etag
11631903794125712047
age
52456
x-content-type-options
nosniff
expires
Mon, 13 Sep 2027 11:36:56 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
date
Sun, 13 Sep 2026 11:36:56 GMT
content-disposition
attachment; filename="f.txt"
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
cache-control
public, immutable, max-age=31536000
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
content-length
216949
x-xss-protection
0
server
cafe
GET
H3
200
pubads_impl.js Show response
securepubads.g.doubleclick.net/pagead/managed/js/gpt/m202609040101/ Frame 14B4
689 KB
0
0ms
0ms
Script
text/javascript
142.251.127.156
Google LLC
General
Full URL
https://securepubads.g.doubleclick.net/pagead/managed/js/gpt/m202609040101/pubads_impl.js?cb=122880985
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.127.156 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfrai-in-f156.1e100.net
Software
cafe /
Resource Hash
37ec5817a0032426b8e9dd7991df9bc48d38d0b4ad358a8890dbe02fb92be13c
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
etag
11631903794125712047
age
52456
x-content-type-options
nosniff
expires
Mon, 13 Sep 2027 11:36:56 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
date
Sun, 13 Sep 2026 11:36:56 GMT
content-disposition
attachment; filename="f.txt"
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
cache-control
public, immutable, max-age=31536000
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
content-length
216949
x-xss-protection
0
server
cafe
GET
H2
200
if.html Show response
silo60.p7cloud.net/ Frame 2244
3 KB
2 KB
71ms
25ms
Document
text/html
2600:9000:26e8:e000:11:a9de:ec0:93a1
Amazon.com
General
Full URL
https://silo60.p7cloud.net/if.html?gdpr=false&gdprConsent=false&tpd=true&md=false
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2600:9000:26e8:e000:11:a9de:ec0:93a1 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
Software
AmazonS3 /
Resource Hash
a05868fe2ac912e68abd58799623f01aa68e8bd4d0afc86c73b17c4528073bb8

Request headers

Referer
https://footyroom.co/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

age
57942
content-encoding
gzip
content-type
text/html
date
Sun, 13 Sep 2026 10:05:32 GMT
etag
W/"916e22881118e2ea1f9740866f5b0119"
last-modified
Fri, 11 Sep 2026 11:16:36 GMT
server
AmazonS3
vary
Accept-Encoding
via
1.1 c6e8f008a950e08db9c0a054276fe95e.cloudfront.net (CloudFront)
x-amz-cf-id
9X522nxpnpkla9iY4P9g4kxA9nwhtUViSVmrquUCAeJjwYRIaGUIGQ==
x-amz-cf-pop
FRA56-P10
x-amz-server-side-encryption
AES256
x-cache
Hit from cloudfront
GET
H2
200
bs1.js Show response
silo60.p7cloud.net/
534 B
821 B
261ms
261ms
Script
application/javascript
2600:9000:26e8:a200:11:a9de:ec0:93a1
Amazon.com
General
Full URL
https://silo60.p7cloud.net/bs1.js?callback=aspan.setIABInit&uri=https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review&rt=p
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2600:9000:26e8:a200:11:a9de:ec0:93a1 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
Software
CloudFront /
Resource Hash
4411aa744346b0a2f2b92b31a84c714a40ee384e60345816a03c253e0cb7db5f

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
public, max-age=14410
via
1.1 adffa554e502bb59dc89f14ddc6170ce.cloudfront.net (CloudFront)
x-cache
Miss from cloudfront
content-length
534
x-amz-cf-id
1BY-sl8ycUFZ8CJvSp7TczfETBtyL_SsGHPiUtCTWTEg4ST-m2KBOA==
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
application/javascript
x-amz-cf-pop
FRA56-P10
server
CloudFront
vary
Origin
GET
H2
200
asp Show response
ua.p7cloud.net/
73 B
328 B
94ms
22ms
Script
application/javascript
2600:9000:2251:f600:15:c08e:ec40:93a1
Amazon.com
General
Full URL
https://ua.p7cloud.net/asp?aspan=YXJjc3Bhbi11c2VyOmFyY3NwYW4tZHJvd3NzYXA
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2600:9000:2251:f600:15:c08e:ec40:93a1 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
Software
CloudFront /
Resource Hash
c5ab5f8a37cdc312ebb05404fe6c193baf2fd064a9ade46f8c6d5b09bd258433

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

age
48310
via
1.1 6fc439c8bc0a64a7ab978ce699795274.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
content-length
73
x-amz-cf-id
4p3yECAQR1Fa5GiZC9u6cls7d5XLUbykjeBhP4gocR_Z3kjyWkzvPg==
date
Sun, 13 Sep 2026 12:46:03 GMT
content-type
application/javascript
x-amz-cf-pop
FRA60-P3
server
CloudFront
GET
H2
200
locdot Show response
location.p7cloud.net/
296 B
580 B
110ms
35ms
Script
application/javascript
2600:9000:28eb:cc00:12:a1d3:a3c0:93a1
Amazon.com
General
Full URL
https://location.p7cloud.net/locdot
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2600:9000:28eb:cc00:12:a1d3:a3c0:93a1 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
Software
CloudFront /
Resource Hash
06703c2a3084400650b4ee792386b425153efa8189a3c8de4458adc7c6446a74

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, no-store, must-revalidate
via
1.1 a95e3ddc09a8118950740e900d11ffc8.cloudfront.net (CloudFront)
x-cache
Miss from cloudfront
content-length
296
x-amz-cf-id
9VRNDlqcM9TjujLEELmSTDt4cMcTN3giUn5seToMkPpqMb7fwRkIGA==
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
application/javascript
x-amz-cf-pop
FRA60-P12
server
CloudFront
GET
H2
200
px.gif Show response
ad-delivery.net/
43 B
110 B
20ms
19ms
Fetch
image/gif
2606:4700:10::ac42:948c
Cloudflare
General
Full URL
https://ad-delivery.net/px.gif?ch=1&e=0.6290094925470635
Requested by
Host: btloader.com
URL: https://btloader.com/tag?o=6278260873756672&upapi=true
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2606:4700:10::ac42:948c -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
cf4724b2f736ed1a0ae6bc28f1ead963d9cd2c1fd87b6ef32e7799fc1c5c8bda

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
5
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=cpEfJQ==, md5=rUsPYG4PhGW8TEwXCzfhow==
cf-cache-status
HIT
etag
"ad4b0f606e0f8465bc4c4c170b37e1a3"
age
2223
x-goog-stored-content-encoding
identity
expires
Mon, 14 Sep 2026 01:56:21 GMT
x-goog-stored-content-length
43
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
image/gif
last-modified
Wed, 05 May 2021 19:25:32 GMT
x-guploader-uploadid
AKhXX7Ij0HsF82F-154UYfFX1Gp5cCmGjgS1xTm34ZQjp8FSns2hC9fd1cFeCxd11HNskCSYP4DIRTI
cache-control
public, max-age=86400
x-goog-storage-class
MULTI_REGIONAL
cf-ray
a3abdc19ce6c8b7c-AMS
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1620242732037093
content-length
43
server
cloudflare
GET
H2
200
grumi.js Show response
rumcdn.geoedge.be/3c5f792e-2099-4b89-b2fa-171ced5152e0/ Frame F450
335 KB
102 KB
26ms
26ms
Script
text/javascript
2600:9000:2013:ac00:4:b37b:9440:93a1
Amazon.com
General
Full URL
https://rumcdn.geoedge.be/3c5f792e-2099-4b89-b2fa-171ced5152e0/grumi.js
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2600:9000:2013:ac00:4:b37b:9440:93a1 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
Software
AmazonS3 /
Resource Hash
9d7e2af808c9eb886aa9a96d4914114a87842afae4fd68a732dae72969fe189d

Request headers

sec-ch-ua-platform
"Linux"
Referer
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
x-amz-version-id
9KlaJQGN9q_j45lE.aPiV3qocEqyV6uf
etag
W/"8f326b089f75349d1da143b09d32db08"
age
1260
x-cache
Hit from cloudfront
x-amz-cf-id
XWLsmPxGqzqSdFNVhjOSv6roZX29DRmBVPxIDtTjm2wGdR9BLWdRmw==
date
Mon, 14 Sep 2026 01:50:14 GMT
content-type
text/javascript
vary
Accept-Encoding
last-modified
Mon, 14 Sep 2026 01:49:52 GMT
cache-control
public,max-age=3600,stale-while-revalidate=3600,immutable,must-revalidate
timing-allow-origin
*
via
1.1 e4a99a83f5512cdd81d7e04f709bb800.cloudfront.net (CloudFront)
x-amz-cf-pop
FRA56-P14
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H2
200
grumi.js Show response
rumcdn.geoedge.be/3c5f792e-2099-4b89-b2fa-171ced5152e0/ Frame 7B71
335 KB
0
21ms
21ms
Script
text/javascript
2600:9000:2013:ac00:4:b37b:9440:93a1
Amazon.com
General
Full URL
https://rumcdn.geoedge.be/3c5f792e-2099-4b89-b2fa-171ced5152e0/grumi.js
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2600:9000:2013:ac00:4:b37b:9440:93a1 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
Software
AmazonS3 /
Resource Hash
9d7e2af808c9eb886aa9a96d4914114a87842afae4fd68a732dae72969fe189d

Request headers

sec-ch-ua-platform
"Linux"
Referer
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
x-amz-version-id
9KlaJQGN9q_j45lE.aPiV3qocEqyV6uf
etag
W/"8f326b089f75349d1da143b09d32db08"
age
1260
x-cache
Hit from cloudfront
x-amz-cf-id
XWLsmPxGqzqSdFNVhjOSv6roZX29DRmBVPxIDtTjm2wGdR9BLWdRmw==
date
Mon, 14 Sep 2026 01:50:14 GMT
content-type
text/javascript
vary
Accept-Encoding
last-modified
Mon, 14 Sep 2026 01:49:52 GMT
cache-control
public,max-age=3600,stale-while-revalidate=3600,immutable,must-revalidate
timing-allow-origin
*
via
1.1 e4a99a83f5512cdd81d7e04f709bb800.cloudfront.net (CloudFront)
x-amz-cf-pop
FRA56-P14
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H2
451
713229.gif Show response
idsync.rlcdn.com/ Frame A2A9
0
79 B
75ms
29ms
Document
text/plain
35.244.174.68
Google LLC
General
Full URL
https://idsync.rlcdn.com/713229.gif?partner_uid=silo60:ae025c43-b265-4e9c-856f-17be8af12f8f
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
35.244.174.68 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
68.174.244.35.bc.googleusercontent.com
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

Referer
https://footyroom.co/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

alt-svc
h3=":443"; ma=2592000
content-length
0
date
Mon, 14 Sep 2026 02:11:13 GMT
via
1.1 google
GET

getuidp
ib.adnxs.com/
0
0


GET
H2
200
cm Show response
us-u.openx.net/w/1.0/ Frame A25C
68 B
273 B
115ms
69ms
Document
text/html
34.98.64.218
Google LLC
General
Full URL
https://us-u.openx.net/w/1.0/cm?id=7f21a24f-7b81-4961-8928-1f1339490a93&gdpr=0&gdpr_consent=&us_privacy=&gpp=&gpp_sid=-1&r=https%3A%2F%2Fsync.p7cloud.net%2Fp.png%3Fopenx_id%3D{OPENX_ID}%26arcid%3Dsilo60%253Aae025c43-b265-4e9c-856f-17be8af12f8f
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.98.64.218 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
218.64.98.34.bc.googleusercontent.com
Software
/
Resource Hash
4cde20607a069eefd4289f5f75cbacac271db09ca6fb9fbfaf615876ee6f9257

Request headers

Referer
https://footyroom.co/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

alt-svc
h3=":443"; ma=2592000
cache-control
private, max-age=0, no-cache
content-length
68
content-type
text/html
date
Mon, 14 Sep 2026 02:11:13 GMT
p3p
CP="CUR ADM OUR NOR STA NID"
pragma
no-cache
vary
Accept, Accept-Encoding
via
1.1 google
x-forwarded-for
193.32.249.159
GET
H2
200
get Show response
vi.ml314.com/
264 B
358 B
83ms
27ms
Script
application/javascript
35.201.104.135
Google LLC
General
Full URL
https://vi.ml314.com/get?eid=70139&tk=4kEzWAtLy3ROjiGWVaT5oYPHFkZ9s5teXcFusAo2hRo3d&fp=
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
35.201.104.135 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
135.104.201.35.bc.googleusercontent.com
Software
Google Frontend /
Resource Hash
9dffbd45ce48bf5e8eeb90b3d8567f8270f217c174de81fe3693d6dcdbaa1588

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=86400, private
content-encoding
br
via
1.1 google
alt-svc
h3=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
application/javascript
vary
Accept-Encoding
server
Google Frontend
GET
H2
200
13333 Show response
d3j8vl19c1131u.cloudfront.net/
31 B
284 B
182ms
126ms
Script
application/javascript
2600:9000:208a:a00:18:f839:ac80:21
Amazon.com
General
Full URL
https://d3j8vl19c1131u.cloudfront.net/13333?uri=ae025c43-b265-4e9c-856f-17be8af12f8f&region=us
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2600:9000:208a:a00:18:f839:ac80:21 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
Software
CloudFront /
Resource Hash
cc07a9f0bd325aa622b9fc0f15ea34b14f61ddbfa9374e2bd91073c7ede137bd

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

via
1.1 7ca1f888e55cc20dcbd40691cd7e4e84.cloudfront.net (CloudFront)
x-cache
LambdaGeneratedResponse from cloudfront
content-length
31
x-amz-cf-id
Fxmv2ZA0ZfSDzVsSx6lW4yki83SeeJAHl3SpCHwbo2KKTMelRfChOA==
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
application/javascript
x-amz-cf-pop
FRA60-P13
server
CloudFront
vary
Origin
GET
H2
200
/ Show response
lal.p7cloud.net/silo60/
153 B
410 B
112ms
22ms
Script
application/javascript
2600:9000:20e8:fa00:3:c079:7fc0:93a1
Amazon.com
General
Full URL
https://lal.p7cloud.net/silo60/?aspan=YXJjc3Bhbi11c2VyOmFyY3NwYW4tZHJvd3NzYXA&SECOND=0&MINUTE=11&HOUR=4&COOKIE=1&DAY=1&BROWSER=1&ENGAGEMENT=0&endpoints=9QW7xNTy/Auto,75fZV4Jd/Auto
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2600:9000:20e8:fa00:3:c079:7fc0:93a1 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
Software
CloudFront /
Resource Hash
178baf0ac7985ada858fb5fcbb47e669b25fbbc752f929fa1e9d640e4cfa1de5

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

age
626407
via
1.1 d6f4f7f6ffad42fddc330a28a55aeffe.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
content-length
153
x-amz-cf-id
HePyEwjI_uQBTbHq37GFyus-D_UElncUofdCNDxiJCIdiimdEG3Knw==
date
Sun, 06 Sep 2026 20:11:06 GMT
content-type
application/javascript
x-amz-cf-pop
FRA56-P13
server
CloudFront
GET
H2
200
check
pixel.tapad.com/idsync/ex/receive/
Redirect Chain
  • https://pixel.tapad.com/idsync/ex/receive?partner_id=3416&partner_device_id=silo60:ae025c43-b265-4e9c-856f-17be8af12f8f
  • https://pixel.tapad.com/idsync/ex/receive/check?partner_id=3416&partner_device_id=silo60:ae025c43-b265-4e9c-856f-17be8af12f8f
95 B
426 B
30ms
29ms
Image
image/png
34.111.113.62
Google LLC
General
Full URL
https://pixel.tapad.com/idsync/ex/receive/check?partner_id=3416&partner_device_id=silo60:ae025c43-b265-4e9c-856f-17be8af12f8f
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Server
34.111.113.62 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
62.113.111.34.bc.googleusercontent.com
Software
/
Resource Hash
3eb10792d1f0c7e07e7248273540f1952d9a5a2996f4b5df70ab026cd9f05517
Security Headers
Name Value
Strict-Transport-Security max-age=31536000

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer
https://footyroom.co/

Response headers

strict-transport-security
max-age=31536000
accept-ch
Sec-CH-UA, Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Mobile, Sec-CH-UA-Model, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version, Sec-CH-UA-WoW64
via
1.1 google
access-control-allow-origin
*
alt-svc
h3=":443"; ma=2592000
p3p
policyref="http://tapad-taptags.s3.amazonaws.com/policy/p3p.xml", CP="NOI DSP COR ADM PSAo PSDo OURo SAMo UNRo OTRo BUS COM NAV DEM STA PRE"
content-length
95
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
image/png

Redirect headers

strict-transport-security
max-age=31536000
location
https://pixel.tapad.com/idsync/ex/receive/check?partner_id=3416&partner_device_id=silo60:ae025c43-b265-4e9c-856f-17be8af12f8f
accept-ch
Sec-CH-UA, Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Mobile, Sec-CH-UA-Model, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version, Sec-CH-UA-WoW64
via
1.1 google
access-control-allow-origin
*
alt-svc
h3=":443"; ma=2592000
p3p
policyref="http://tapad-taptags.s3.amazonaws.com/policy/p3p.xml", CP="NOI DSP COR ADM PSAo PSDo OURo SAMo UNRo OTRo BUS COM NAV DEM STA PRE"
content-length
0
date
Mon, 14 Sep 2026 02:11:13 GMT
GET
H2
200
UCookieSetPug
image6.pubmatic.com/AdServer/
0
193 B
96ms
21ms
Image
text/html
103.231.98.107
PubMatic
General
Full URL
https://image6.pubmatic.com/AdServer/UCookieSetPug?p=167693&gdpr=0&gdpr_consent=&us_privacy=&gpp=&gpp_sid=-1&rd=https%3A%2F%2Fsync.p7cloud.net%2Fp.png%3Farcid%3Dsilo60%253Aae025c43-b265-4e9c-856f-17be8af12f8f%26UID%3D%23PM_USER_ID
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
103.231.98.107 , Japan, ASN62713 (AS-PUBMATIC - PubMatic, Inc., US),
Reverse DNS
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=16070400; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=16070400; includeSubDomains
content-length
0
p3p
CP="NOI DSP COR LAW CUR ADMo DEVo TAIo PSAo PSDo IVAo IVDo HISo OTPo OUR SAMo BUS UNI COM NAV INT DEM CNT STA PRE LOC"
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
text/html; charset=UTF-8
GET
H/1.1
204
No Content
token
pixel.rubiconproject.com/ Frame 2244
0
214 B
102ms
23ms
Image
text/plain
69.173.144.165
Magnite
General
Full URL
https://pixel.rubiconproject.com/token?pid=72363&gdpr=0&gdpr_consent=&us_privacy=&gpp=&gpp_sid=-1
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
HTTP/1.1
Security
TLS 1.2, RSA, AES_256_GCM
Server
69.173.144.165 , Germany, ASN26667 (RUBICONPROJECT - Magnite, Inc., US),
Reverse DNS
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://silo60.p7cloud.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

Expires
0
Cache-Control
no-cache,no-store,must-revalidate
P3P
CP="NOI CURa ADMa DEVa TAIa OUR BUS IND UNI COM NAV INT"
X-RPHost
f26806c8bdda8c5582b46025254545cb
Pragma
no-cache
GET
H2
200
720 Show response
a.ad.gt/api/v1/u/matches/
Redirect Chain
  • https://cdn.hadronid.net/hadron.js?url=https%3A%2F%2Ffootyroom.co%2Fmatches%2F80034717%2Fmanchester-united-vs-sabah-fk%2Freview&ref=&_it=amazon&partner_id=720
  • https://a.ad.gt/api/v1/u/matches/720?_it=nitro
6 KB
3 KB
85ms
26ms
Script
application/javascript
2606:4700:10::6814:2396
Cloudflare
General
Full URL
https://a.ad.gt/api/v1/u/matches/720?_it=nitro
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H2
Server
2606:4700:10::6814:2396 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
1b7e701706f765d9c424566f23012446200c4731de24d1616d656d61ed252055

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer
https://footyroom.co/

Response headers

cache-control
max-age=7200
content-encoding
gzip
cf-cache-status
HIT
age
3254
cross-origin-resource-policy
cross-origin
cf-ray
a3abdc1b588e8b43-AMS
date
Mon, 14 Sep 2026 02:11:13 GMT
last-modified
Mon, 14 Sep 2026 01:17:00 GMT
content-type
application/javascript
vary
accept-encoding
server
cloudflare

Redirect headers

cf-ray
a3abdc1aecde66b7-AMS
location
https://a.ad.gt/api/v1/u/matches/720?_it=nitro
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
text/html; charset=UTF-8
server
cloudflare
GET
H2
200
id5-api.js Show response
cdn.id5-sync.com/api/1.0/
117 KB
34 KB
60ms
20ms
Script
text/javascript
2606:4700:10::ac42:a937
Cloudflare
General
Full URL
https://cdn.id5-sync.com/api/1.0/id5-api.js
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2606:4700:10::ac42:a937 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
18120a6bee05cd823d5f4ab0c52006863a059a5d6c535c790a31bdd2ee8c45e7
Security Headers
Name Value
Strict-Transport-Security max-age=15552000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-amz-id-2
DHiDYFKRDSfkx6YgqSzIV/Zzo74NysKK/+Y2b7etBVckx1FUt8JgEgkpS0DInBVh0LromRZthumKMlbaGqBx2p9tSOP2h4tj
strict-transport-security
max-age=15552000; includeSubDomains; preload
cache-control
public, max-age=3600
content-encoding
br
cf-cache-status
HIT
etag
W/"78d670c3a2facd95b81a836b6857d830"
age
398
x-amz-request-id
WD952JCCAEC4W9P8
cf-ray
a3abdc1abb25fba8-AMS
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
text/javascript;charset=utf-8
last-modified
Wed, 18 Mar 2026 12:22:23 GMT
server
cloudflare
x-amz-server-side-encryption
AES256
GET
H2
200
sync.min.js Show response
tags.crwdcntrl.net/lt/c/16576/
45 KB
14 KB
89ms
27ms
Script
text/javascript
13.226.244.59
Amazon.com
General
Full URL
https://tags.crwdcntrl.net/lt/c/16576/sync.min.js
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
13.226.244.59 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-13-226-244-59.fra56.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
4f5a68894720ca8cfd19bb5ab499e5c83fa7de051a4bb037494e589999be8247

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
cache-control
public, max-age=86400
content-encoding
gzip
etag
W/"89c4cdf4522b5ffedfaac19bafbe0081"
age
82044
via
1.1 94bd75b95472ec61935815aa61472392.cloudfront.net (CloudFront)
alt-svc
h3=":443"; ma=86400
x-cache
Hit from cloudfront
x-amz-cf-id
qr0BvM8tNA2K3ybSgfXPSCnY9NyO1MAtfbdjXmJm4mZoYb92evYWag==
date
Mon, 14 Sep 2026 01:06:10 GMT
content-type
text/javascript
last-modified
Thu, 25 Jun 2026 15:51:54 GMT
server
AmazonS3
x-amz-cf-pop
FRA56-P14
x-amz-server-side-encryption
AES256
GET
H/1.1
200
OK
pubcid.min.js Show response
secure.cdn.fastclick.net/js/pubcid/latest/
67 KB
22 KB
137ms
34ms
Script
application/javascript
2.16.241.214
AKAMAI-ASN1 Akama...
General
Full URL
https://secure.cdn.fastclick.net/js/pubcid/latest/pubcid.min.js
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_256_GCM
Server
2.16.241.214 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a2-16-241-214.deploy.static.akamaitechnologies.com
Software
Apache /
Resource Hash
45bc6978e281a938d9485dcbf0859159b24e2f7c9b8b0fafc120b9606e0ea8b1

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

Cache-Control
max-age=900
Content-Encoding
gzip
ETag
"10ab4-63a0ee37f7c40-gzip"
Connection
keep-alive
Expires
Mon, 14 Sep 2026 02:26:13 GMT
Accept-Ranges
bytes
Content-Length
21994
Date
Mon, 14 Sep 2026 02:11:13 GMT
Last-Modified
Wed, 16 Jul 2025 17:04:41 GMT
Content-Type
application/javascript
Server
Apache
Vary
Accept-Encoding
GET
H3
200
gpt
securepubads.g.doubleclick.net/pagead/managed/dict/m202609080101/
64 KB
22 KB
39ms
38ms
Other
text/plain
142.251.127.156
Google LLC
General
Full URL
https://securepubads.g.doubleclick.net/pagead/managed/dict/m202609080101/gpt
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.127.156 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfrai-in-f156.1e100.net
Software
cafe /
Resource Hash
0579619786f40ef19b66506851c5d4a0e65b1d04212419bb8f9b14adac695f0c
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
etag
12366465561172195219
age
52686
x-content-type-options
nosniff
expires
Sun, 20 Sep 2026 11:33:07 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
date
Sun, 13 Sep 2026 11:33:07 GMT
content-type
text/plain; charset=UTF-8
vary
Accept-Encoding
cache-control
public, immutable, max-age=604800, stale-while-revalidate=7200
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
content-length
22504
x-xss-protection
0
server
cafe
use-as-dictionary
match="/gampad/ads?*ptt=17*", id="m202609080101"
GET
H3
200
gpt
securepubads.g.doubleclick.net/pagead/managed/dict/m202609080101/ Frame 9E78
64 KB
0
35ms
35ms
Other
text/plain
142.251.127.156
Google LLC
General
Full URL
https://securepubads.g.doubleclick.net/pagead/managed/dict/m202609080101/gpt
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.127.156 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfrai-in-f156.1e100.net
Software
cafe /
Resource Hash
0579619786f40ef19b66506851c5d4a0e65b1d04212419bb8f9b14adac695f0c
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
etag
12366465561172195219
age
52686
x-content-type-options
nosniff
expires
Sun, 20 Sep 2026 11:33:07 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
date
Sun, 13 Sep 2026 11:33:07 GMT
content-type
text/plain; charset=UTF-8
vary
Accept-Encoding
cache-control
public, immutable, max-age=604800, stale-while-revalidate=7200
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
content-length
22504
x-xss-protection
0
server
cafe
use-as-dictionary
match="/gampad/ads?*ptt=17*", id="m202609080101"
GET
H3
200
gpt
securepubads.g.doubleclick.net/pagead/managed/dict/m202609080101/ Frame 14B4
64 KB
0
38ms
38ms
Other
text/plain
142.251.127.156
Google LLC
General
Full URL
https://securepubads.g.doubleclick.net/pagead/managed/dict/m202609080101/gpt
Requested by
Host: footyroom.co
URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.127.156 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfrai-in-f156.1e100.net
Software
cafe /
Resource Hash
0579619786f40ef19b66506851c5d4a0e65b1d04212419bb8f9b14adac695f0c
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
etag
12366465561172195219
age
52686
x-content-type-options
nosniff
expires
Sun, 20 Sep 2026 11:33:07 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
date
Sun, 13 Sep 2026 11:33:07 GMT
content-type
text/plain; charset=UTF-8
vary
Accept-Encoding
cache-control
public, immutable, max-age=604800, stale-while-revalidate=7200
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
content-length
22504
x-xss-protection
0
server
cafe
use-as-dictionary
match="/gampad/ads?*ptt=17*", id="m202609080101"
GET
H3
200
overlay- Show response
fundingchoicesmessages.google.com/f/AGSKWxWZhNx2_1gAwcoGz-Jt5z2bUEn6DGtACsm22sAAOzACGpcnRNB-aV7NmMrlRvIhD-hKaKnvpjj58g3iZ_w6LEawKg-jT4kO0FdBCqjS7vKFRDpjZg3m68LWJrCzF-syUrgWi7gHrNn5yJh-fvB1mNCQPw2OY...
54 B
109 B
55ms
54ms
Script
application/javascript
142.251.110.100
Google LLC
General
Full URL
https://fundingchoicesmessages.google.com/f/AGSKWxWZhNx2_1gAwcoGz-Jt5z2bUEn6DGtACsm22sAAOzACGpcnRNB-aV7NmMrlRvIhD-hKaKnvpjj58g3iZ_w6LEawKg-jT4kO0FdBCqjS7vKFRDpjZg3m68LWJrCzF-syUrgWi7gHrNn5yJh-fvB1mNCQPw2OYX-x7PSD0CifCt7vY_wDI9cnu6D8ea0_/_/adiframe18..adinject./ad/live-/ads/ad_/ads/overlay-
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.110.100 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f100.1e100.net
Software
ESF /
Resource Hash
99b8168901ae10ac07f3a2dfb99688ce9ccebad0c01b3f245f995d075d6075e1
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script';report-uri /_/ContributorServingWebSwitchboardHttp/cspreport, script-src 'report-sample' 'nonce-65EuUihIT6D8NfZc01DnPA' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/ContributorServingWebSwitchboardHttp/cspreport;worker-src 'self', script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/ContributorServingWebSwitchboardHttp/cspreport/allowlist
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-content-type-options
nosniff
expires
Mon, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
application/javascript; charset=utf-8
x-frame-options
SAMEORIGIN
reporting-endpoints
default="/_/ContributorServingWebSwitchboardHttp/web-reports?context=eJzjStHikmII1pBiaL15jnU6EJcsOs_aBsRdQDwHiA0VLrE6A_GH-susP4C4SOIKawsQf6q6wSpSfYP1W7EvG0eJLxvLW3-2hdMC2VYCsYhBEJsMEKcdDGfLA2IhHo6D6-deZRN4sejxZSYljaT8wvjk_LySosyk0pL8orTktNTi1KKy1KJ4IwMjMwNLA0s9Q8P4AgMA_Y87Qw"
content-security-policy
require-trusted-types-for 'script';report-uri /_/ContributorServingWebSwitchboardHttp/cspreport, script-src 'report-sample' 'nonce-65EuUihIT6D8NfZc01DnPA' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/ContributorServingWebSwitchboardHttp/cspreport;worker-src 'self', script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/ContributorServingWebSwitchboardHttp/cspreport/allowlist
cache-control
no-cache, no-store, max-age=0, must-revalidate
cross-origin-opener-policy
same-origin
pragma
no-cache
accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
cross-origin-resource-policy
cross-origin
permissions-policy
ch-ua-arch=*, ch-ua-bitness=*, ch-ua-full-version=*, ch-ua-full-version-list=*, ch-ua-model=*, ch-ua-wow64=*, ch-ua-form-factors=*, ch-ua-platform=*, ch-ua-platform-version=*
x-xss-protection
0
server
ESF
GET
H3
200
rum.js Show response
pagead2.googlesyndication.com/pagead/js/
82 KB
29 KB
93ms
40ms
Script
text/javascript
142.251.20.154
Google LLC
General
Full URL
https://pagead2.googlesyndication.com/pagead/js/rum.js?fcd=true
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.20.154 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bx-in-f154.1e100.net
Software
cafe /
Resource Hash
b92d631998d0b44cc058cdc300030cc9dc0b19d0ba45dde0f0eba3bc18aea237
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
etag
9013868146048828519
age
1090
x-content-type-options
nosniff
expires
Mon, 14 Sep 2026 02:53:03 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
date
Mon, 14 Sep 2026 01:53:03 GMT
content-disposition
attachment; filename="f.txt"
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
cache-control
public, max-age=3600
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
content-length
30091
x-xss-protection
0
server
cafe
POST
H3
204
AGSKWxXcIhhbiu358SLpLSZn6QOYaPbwlxav7jRknBPngNDhiu-aHpWWnD2iRf3rbMleS48-7r4S1XoPT6c4gZz2exbyv7UHl-eY0YIPBUvEy2yfJ-HmYY3As4TrqkAoX_Vlr7ImJsCCaQ== Show response
fundingchoicesmessages.google.com/el/
0
28 B
53ms
53ms
XHR
text/html
142.251.110.100
Google LLC
General
Full URL
https://fundingchoicesmessages.google.com/el/AGSKWxXcIhhbiu358SLpLSZn6QOYaPbwlxav7jRknBPngNDhiu-aHpWWnD2iRf3rbMleS48-7r4S1XoPT6c4gZz2exbyv7UHl-eY0YIPBUvEy2yfJ-HmYY3As4TrqkAoX_Vlr7ImJsCCaQ==
Requested by
Host:
URL: /_/mss/boq-content-ads-contributor/_/js/k=boq-content-ads-contributor.ContributorServingResponseClientJs.nl.vyMVZXSm2Sw.es5.O/d=1/rs=AJlcJMwT-z7-Ua2kRQtmTjsz1eye77FxMQ/m=kernel_loader,loader_js_executable
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.110.100 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f100.1e100.net
Software
ESF /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script';report-uri /_/ContributorLoggingHttp/cspreport, script-src 'report-sample' 'nonce-b09Knrisu5YcU5zdN6tFUg' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/ContributorLoggingHttp/cspreport;worker-src 'self', script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/ContributorLoggingHttp/cspreport/allowlist
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
text/plain
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
86400
access-control-allow-methods
POST, GET, OPTIONS
x-content-type-options
nosniff
expires
Mon, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
text/html; charset=utf-8
x-frame-options
SAMEORIGIN
reporting-endpoints
default="/_/ContributorLoggingHttp/web-reports?context=eJzj0tDikmLw15Bi-FB_mfUHEC-cFsi2EohFDILYZIA47WA4Wx4QC_FwHFw_9yqbwIemi5eZlFyS8gvjk_PzSlLzSnQTU4p1QeyizKTSkvwiFHZqGUhFTn56emZeeryRgZGZgaWBpZ6hQXyBAQDpSCx1"
content-security-policy
require-trusted-types-for 'script';report-uri /_/ContributorLoggingHttp/cspreport, script-src 'report-sample' 'nonce-b09Knrisu5YcU5zdN6tFUg' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/ContributorLoggingHttp/cspreport;worker-src 'self', script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/ContributorLoggingHttp/cspreport/allowlist
cache-control
no-cache, no-store, max-age=0, must-revalidate
cross-origin-opener-policy
same-origin
pragma
no-cache
accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
access-control-allow-credentials
true
permissions-policy
ch-ua-arch=*, ch-ua-bitness=*, ch-ua-full-version=*, ch-ua-full-version-list=*, ch-ua-model=*, ch-ua-wow64=*, ch-ua-form-factors=*, ch-ua-platform=*, ch-ua-platform-version=*
access-control-allow-origin
https://footyroom.co
content-length
0
x-xss-protection
0
server
ESF
GET
H2
200
px.gif Show response
ad-delivery.net/
43 B
114 B
20ms
19ms
Fetch
image/gif
2606:4700:10::ac42:948c
Cloudflare
General
Full URL
https://ad-delivery.net/px.gif?ch=2&e=0.049541276422894964
Requested by
Host: btloader.com
URL: https://btloader.com/tag?o=6278260873756672&upapi=true
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2606:4700:10::ac42:948c -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
cf4724b2f736ed1a0ae6bc28f1ead963d9cd2c1fd87b6ef32e7799fc1c5c8bda

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
5
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=cpEfJQ==, md5=rUsPYG4PhGW8TEwXCzfhow==
cf-cache-status
HIT
etag
"ad4b0f606e0f8465bc4c4c170b37e1a3"
age
2224
x-goog-stored-content-encoding
identity
expires
Mon, 14 Sep 2026 01:56:21 GMT
x-goog-stored-content-length
43
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
image/gif
last-modified
Wed, 05 May 2021 19:25:32 GMT
x-guploader-uploadid
AKhXX7Ij0HsF82F-154UYfFX1Gp5cCmGjgS1xTm34ZQjp8FSns2hC9fd1cFeCxd11HNskCSYP4DIRTI
cache-control
public, max-age=86400
x-goog-storage-class
MULTI_REGIONAL
cf-ray
a3abdc1ae8e18b7c-AMS
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1620242732037093
content-length
43
server
cloudflare
GET
H3
200
favicon.ico Show response
ad.doubleclick.net/
1 KB
129 B
53ms
52ms
Fetch
image/x-icon
142.251.14.149
Google LLC
General
Full URL
https://ad.doubleclick.net/favicon.ico?ad=300x250&ad_box_=1&adnet=1&showad=1&size=250x250&e=0.32681835273676596
Requested by
Host: btloader.com
URL: https://btloader.com/tag?o=6278260873756672&upapi=true
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.14.149 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f149.1e100.net
Software
sffe /
Resource Hash
d961b08e4321250926de6f79087594975fe20ad1518de8f91eb711af5d1a6ef8
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
report-to
{"group":"ads-doubleclick-media","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/ads-doubleclick-media"}]}
x-content-type-options
nosniff
expires
Tue, 15 Sep 2026 02:11:13 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
image/x-icon
vary
Accept-Encoding
last-modified
Tue, 08 May 2012 13:08:06 GMT
cache-control
public, max-age=86400
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to="ads-doubleclick-media"
content-length
104
x-xss-protection
0
server
sffe
POST
H3
204
AGSKWxXcIhhbiu358SLpLSZn6QOYaPbwlxav7jRknBPngNDhiu-aHpWWnD2iRf3rbMleS48-7r4S1XoPT6c4gZz2exbyv7UHl-eY0YIPBUvEy2yfJ-HmYY3As4TrqkAoX_Vlr7ImJsCCaQ== Show response
fundingchoicesmessages.google.com/el/
0
28 B
59ms
58ms
XHR
text/html
142.251.110.100
Google LLC
General
Full URL
https://fundingchoicesmessages.google.com/el/AGSKWxXcIhhbiu358SLpLSZn6QOYaPbwlxav7jRknBPngNDhiu-aHpWWnD2iRf3rbMleS48-7r4S1XoPT6c4gZz2exbyv7UHl-eY0YIPBUvEy2yfJ-HmYY3As4TrqkAoX_Vlr7ImJsCCaQ==
Requested by
Host:
URL: /_/mss/boq-content-ads-contributor/_/js/k=boq-content-ads-contributor.ContributorServingResponseClientJs.nl.vyMVZXSm2Sw.es5.O/d=1/rs=AJlcJMwT-z7-Ua2kRQtmTjsz1eye77FxMQ/m=kernel_loader,loader_js_executable
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.110.100 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f100.1e100.net
Software
ESF /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Content-Security-Policy script-src 'report-sample' 'nonce-32lHIs5QyPYPUsiPPNZUGg' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/ContributorLoggingHttp/cspreport;worker-src 'self', script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/ContributorLoggingHttp/cspreport/allowlist, require-trusted-types-for 'script';report-uri /_/ContributorLoggingHttp/cspreport
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
text/plain
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
86400
access-control-allow-methods
POST, GET, OPTIONS
x-content-type-options
nosniff
expires
Mon, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
text/html; charset=utf-8
x-frame-options
SAMEORIGIN
reporting-endpoints
default="/_/ContributorLoggingHttp/web-reports?context=eJzj0tDikmLw15Bi-FB_mfUHEC-cFsi2EohFDILYZIA47WA4Wx4QC_FwHFw_9yqbwIqPD94xKbkk5RfGJ-fnlaTmlegmphTrgthFmUmlJflFKOzUMpCKnPz09My89HgjAyMzA0sDSz1Dg_gCAwAANCzG"
content-security-policy
script-src 'report-sample' 'nonce-32lHIs5QyPYPUsiPPNZUGg' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/ContributorLoggingHttp/cspreport;worker-src 'self', script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/ContributorLoggingHttp/cspreport/allowlist, require-trusted-types-for 'script';report-uri /_/ContributorLoggingHttp/cspreport
cache-control
no-cache, no-store, max-age=0, must-revalidate
cross-origin-opener-policy
same-origin
pragma
no-cache
accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
access-control-allow-credentials
true
permissions-policy
ch-ua-arch=*, ch-ua-bitness=*, ch-ua-full-version=*, ch-ua-full-version-list=*, ch-ua-model=*, ch-ua-wow64=*, ch-ua-form-factors=*, ch-ua-platform=*, ch-ua-platform-version=*
access-control-allow-origin
https://footyroom.co
content-length
0
x-xss-protection
0
server
ESF
GET
H2
200
bridge3.789.0_en.html Show response
imasdk.googleapis.com/js/core/ Frame 6E46
960 KB
285 KB
121ms
38ms
Document
text/html
2a00:1450:4001:c15::5f
Google LLC
General
Full URL
https://imasdk.googleapis.com/js/core/bridge3.789.0_en.html
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a00:1450:4001:c15::5f Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
1ebb685e3aec008b3c941ea272149fa403a676e89235c76dc2c1f9e62db1430f
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://footyroom.co/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

accept-ranges
bytes
age
383026
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cache-control
public, max-age=31536000
content-encoding
gzip
content-length
291668
content-type
text/html
cross-origin-opener-policy
same-origin; report-to="ads-doubleclick-instream-static"
cross-origin-resource-policy
cross-origin
date
Wed, 09 Sep 2026 15:47:27 GMT
expires
Thu, 09 Sep 2027 15:47:27 GMT
last-modified
Wed, 09 Sep 2026 14:29:10 GMT
report-to
{"group":"ads-doubleclick-instream-static","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/ads-doubleclick-instream-static"}]}
server
sffe
vary
Accept-Encoding
x-content-type-options
nosniff
x-xss-protection
0
GET
H2
200
client.js Show response
s0.2mdn.net/instream/video/ Frame 9E78
44 KB
17 KB
139ms
49ms
Script
text/javascript
2a00:1450:4001:c25::95
Google LLC
General
Full URL
https://s0.2mdn.net/instream/video/client.js
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a00:1450:4001:c25::95 Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
d0bffc7261df1454c5e05475cda7d9e6647318dc6c3936767e1252bfe8849c54
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
private, max-age=900
content-encoding
gzip
cross-origin-resource-policy
cross-origin
report-to
{"group":"ads-doubleclick-media","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/ads-doubleclick-media"}]}
x-content-type-options
nosniff
expires
Mon, 14 Sep 2026 02:11:13 GMT
accept-ranges
bytes
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cross-origin-opener-policy-report-only
same-origin; report-to="ads-doubleclick-media"
content-length
16746
date
Mon, 14 Sep 2026 02:11:13 GMT
x-xss-protection
0
content-type
text/javascript
vary
Accept-Encoding
server
sffe
GET
H2
200
latest.json Show response
cdn.jsdelivr.net/gh/prebid/currency-file@1/ Frame 22B1
2 KB
1 KB
53ms
14ms
Fetch
application/json
2a04:4e42:400::485
Fastly
General
Full URL
https://cdn.jsdelivr.net/gh/prebid/currency-file@1/latest.json?date=20260914
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a04:4e42:400::485 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
/
Resource Hash
46f2212adc3d46f1cf1c201e95361d29258a5bc2f0f6d1c550d4482d2030b04d
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
content-type
text/plain
sec-ch-ua-mobile
?0

Response headers

access-control-expose-headers
*
content-encoding
br
etag
W/"609-apL2839xlGdmK++22Uv8md5Tb2A"
age
40234
x-content-type-options
nosniff
x-jsd-version-type
version
alt-svc
h3=":443";ma=86400,h3-29=":443";ma=86400,h3-27=":443";ma=86400
x-cache
HIT, HIT
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
application/json; charset=utf-8
x-served-by
cache-fra-eddf8230081-FRA, cache-rtm-ehrd2290057-RTM
vary
Accept-Encoding
strict-transport-security
max-age=31536000; includeSubDomains; preload
cache-control
public, max-age=604800, s-maxage=43200
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
content-length
806
x-jsd-version
1.0.2914
GET
H2
200
pbhid Show response
id.hadron.ad.gt/api/v1/ Frame 22B1
2 B
271 B
179ms
120ms
Fetch
application/json
2606:4700:10::6814:2396
Cloudflare
General
Full URL
https://id.hadron.ad.gt/api/v1/pbhid?partner_id=574&_it=prebid&t=1&src=id&domain=footyroom.co&us_privacy=1---
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2606:4700:10::6814:2396 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
44136fa355b3678a1146ad16f7e8649e94fb4fc21fe77e8310c060f61caaff8a

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
content-type
text/plain
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=604800
cf-cache-status
DYNAMIC
access-control-allow-credentials
true
access-control-allow-methods
HEAD,GET,POST,PUT,DELETE,OPTIONS
cf-ray
a3abdc1bceb30e48-AMS
access-control-allow-origin
*
content-length
2
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
application/json; charset=utf8
server
cloudflare
access-control-allow-headers
authorization,content-type
POST
H2
200
prebid Show response
id5-sync.com/api/config/ Frame 22B1
195 B
651 B
81ms
22ms
Fetch
application/json
135.125.170.108
OVH OVH SAS
General
Full URL
https://id5-sync.com/api/config/prebid
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
135.125.170.108 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
ns3270108.ip-135-125-170.eu
Software
/
Resource Hash
61407ce1df311cd5bcff27d026e281a184a2cffe8fa24c3a2758ed2f2624b317
Security Headers
Name Value
Strict-Transport-Security max-age=63072000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=63072000; includeSubDomains; preload
content-encoding
gzip
access-control-allow-credentials
true
access-control-allow-origin
https://footyroom.co
p3p
CP="CAO PSA OUR"
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
application/json;charset=UTF-8
vary
origin,access-control-request-method,access-control-request-headers,accept-encoding
GET
H2
200
rid Show response
match.adsrvr.org/track/ Frame 22B1
63 B
423 B
90ms
28ms
Fetch
application/json
52.223.40.198
Amazon.com
General
Full URL
https://match.adsrvr.org/track/rid?ttd_pid=9t8jzll&fmt=json
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
52.223.40.198 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
a6370ebea231e0c9a.awsglobalaccelerator.com
Software
Kestrel /
Resource Hash
eff5a4b24cdbdc1f0ce7c7619eef45d704bf196d6583499ce9d5e242dd57dfa9

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
content-type
text/plain
sec-ch-ua-mobile
?0

Response headers

cache-control
private
content-encoding
gzip
access-control-allow-credentials
true
expires
Wed, 14 Oct 2026 02:11:13 GMT
access-control-allow-origin
https://footyroom.co
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
application/json
vary
Origin,Accept-Encoding
server
Kestrel
access-control-allow-headers
Origin, X-Requested-With, Content-Type, Content-Length, Content-Encoding, Vary, Cache-Control, Accept, x-integration-type
GET
H2
200
pbhid Show response
id.hadron.ad.gt/api/v1/ Frame 22B1
2 B
0
178ms
178ms
Fetch
application/json
2606:4700:10::6814:2396
Cloudflare
General
Full URL
https://id.hadron.ad.gt/api/v1/pbhid?partner_id=574&_it=prebid&t=1&src=id&domain=footyroom.co&us_privacy=1---
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2606:4700:10::6814:2396 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
44136fa355b3678a1146ad16f7e8649e94fb4fc21fe77e8310c060f61caaff8a

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
content-type
text/plain
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=604800
cf-cache-status
DYNAMIC
access-control-allow-credentials
true
access-control-allow-methods
HEAD,GET,POST,PUT,DELETE,OPTIONS
cf-ray
a3abdc1bceb30e48-AMS
access-control-allow-origin
*
content-length
2
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
application/json; charset=utf8
server
cloudflare
access-control-allow-headers
authorization,content-type
POST
H2
200
prebid Show response
id5-sync.com/api/config/ Frame 22B1
195 B
650 B
98ms
41ms
Fetch
application/json
135.125.170.108
OVH OVH SAS
General
Full URL
https://id5-sync.com/api/config/prebid
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
135.125.170.108 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
ns3270108.ip-135-125-170.eu
Software
/
Resource Hash
61407ce1df311cd5bcff27d026e281a184a2cffe8fa24c3a2758ed2f2624b317
Security Headers
Name Value
Strict-Transport-Security max-age=63072000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=63072000; includeSubDomains; preload
content-encoding
gzip
access-control-allow-credentials
true
access-control-allow-origin
https://footyroom.co
p3p
CP="CAO PSA OUR"
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
application/json;charset=UTF-8
vary
origin,access-control-request-method,access-control-request-headers,accept-encoding
GET
H2
200
rid Show response
match.adsrvr.org/track/ Frame 22B1
63 B
0
89ms
89ms
Fetch
application/json
52.223.40.198
Amazon.com
General
Full URL
https://match.adsrvr.org/track/rid?ttd_pid=9t8jzll&fmt=json
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
52.223.40.198 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
a6370ebea231e0c9a.awsglobalaccelerator.com
Software
Kestrel /
Resource Hash
eff5a4b24cdbdc1f0ce7c7619eef45d704bf196d6583499ce9d5e242dd57dfa9

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
content-type
text/plain
sec-ch-ua-mobile
?0

Response headers

cache-control
private
content-encoding
gzip
access-control-allow-credentials
true
expires
Wed, 14 Oct 2026 02:11:13 GMT
access-control-allow-origin
https://footyroom.co
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
application/json
vary
Origin,Accept-Encoding
server
Kestrel
access-control-allow-headers
Origin, X-Requested-With, Content-Type, Content-Length, Content-Encoding, Vary, Cache-Control, Accept, x-integration-type
POST
H2
204
ortb Show response
srv.scalibur.io/adserver/ Frame 9E78
0
210 B
62ms
60ms
XHR
text/plain
185.167.98.14
CloudWebManage-EU...
General
Full URL
https://srv.scalibur.io/adserver/ortb?type=unit&cb=1789351873823_t6c3wl
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/adunit?id=56&width=970&height=90&url=https%3A%2F%2Ffootyroom.co%2Fmatches%2F80034717%2Fmanchester-united-vs-sabah-fk%2Freview&sids=%7B%7D&schain=1.0%2C1!nitropay.com%2C1728%2C1%2C%2C%2C&containerId=Match%20Highlights-isolated&isDebug=0&cb=1789351873336_kzlsm4&us_privacy=1---&keyValues=%7B%22gamAdUnitId%22%3A%22%2F308365556%2C22913055933%2Fnitro-banner%2Fnitro-banner-2321%22%2C%22ttdPubId%22%3A%221728%22%2C%22siteId%22%3A%222321%22%2C%22nitro_gpid%22%3A%22Match%20Highlights%22%7D
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
185.167.98.14 Amsterdam, Netherlands, ASN41436 (CloudWebManage-EU Kamatera Inc, US),
Reverse DNS
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
no-cache, no-store, must-revalidate
pragma
no-cache
age
0
access-control-allow-credentials
true
expires
0
access-control-allow-origin
https://footyroom.co
date
Mon, 14 Sep 2026 02:11:13 GMT
GET
H3
200
omweb-v1.js Show response
pagead2.googlesyndication.com/omsdk/releases/live/ Frame FEB5
48 KB
17 KB
40ms
40ms
Script
text/javascript
142.251.20.154
Google LLC
General
Full URL
https://pagead2.googlesyndication.com/omsdk/releases/live/omweb-v1.js
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.20.154 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bx-in-f154.1e100.net
Software
sffe /
Resource Hash
6edb5275ff2227bece0bf3341bdabb6f2f6d8ff1fb31d726d263eb317996f4b3
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
age
535
report-to
{"group":"omsdk-team-release-policy","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/omsdk-team-release-policy"}]}
x-content-type-options
nosniff
expires
Mon, 14 Sep 2026 03:02:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:02:18 GMT
last-modified
Tue, 01 Sep 2026 17:39:54 GMT
content-type
text/javascript
vary
Accept-Encoding
cache-control
public, max-age=3600
cross-origin-opener-policy
same-origin; report-to="omsdk-team-release-policy"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/omsdk-team-release-policy
accept-ranges
bytes
content-length
17052
x-xss-protection
0
server
sffe
GET
H2
200
bridge3.789.0_en.html Show response
imasdk.googleapis.com/js/core/ Frame 0AB7
960 KB
0
82ms
82ms
Document
text/html
2a00:1450:4001:c15::5f
Google LLC
General
Full URL
https://imasdk.googleapis.com/js/core/bridge3.789.0_en.html
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a00:1450:4001:c15::5f Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
1ebb685e3aec008b3c941ea272149fa403a676e89235c76dc2c1f9e62db1430f
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://footyroom.co/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

accept-ranges
bytes
age
383026
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cache-control
public, max-age=31536000
content-encoding
gzip
content-length
291668
content-type
text/html
cross-origin-opener-policy
same-origin; report-to="ads-doubleclick-instream-static"
cross-origin-resource-policy
cross-origin
date
Wed, 09 Sep 2026 15:47:27 GMT
expires
Thu, 09 Sep 2027 15:47:27 GMT
last-modified
Wed, 09 Sep 2026 14:29:10 GMT
report-to
{"group":"ads-doubleclick-instream-static","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/ads-doubleclick-instream-static"}]}
server
sffe
vary
Accept-Encoding
x-content-type-options
nosniff
x-xss-protection
0
GET
H2
200
client.js Show response
s0.2mdn.net/instream/video/ Frame 14B4
44 KB
0
103ms
103ms
Script
text/javascript
2a00:1450:4001:c25::95
Google LLC
General
Full URL
https://s0.2mdn.net/instream/video/client.js
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a00:1450:4001:c25::95 Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
d0bffc7261df1454c5e05475cda7d9e6647318dc6c3936767e1252bfe8849c54
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
private, max-age=900
content-encoding
gzip
cross-origin-resource-policy
cross-origin
report-to
{"group":"ads-doubleclick-media","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/ads-doubleclick-media"}]}
x-content-type-options
nosniff
expires
Mon, 14 Sep 2026 02:11:13 GMT
accept-ranges
bytes
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cross-origin-opener-policy-report-only
same-origin; report-to="ads-doubleclick-media"
content-length
16746
date
Mon, 14 Sep 2026 02:11:13 GMT
x-xss-protection
0
content-type
text/javascript
vary
Accept-Encoding
server
sffe
GET
H2
200
latest.json Show response
cdn.jsdelivr.net/gh/prebid/currency-file@1/ Frame A4C8
2 KB
0
24ms
24ms
Fetch
application/json
2a04:4e42:400::485
Fastly
General
Full URL
https://cdn.jsdelivr.net/gh/prebid/currency-file@1/latest.json?date=20260914
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a04:4e42:400::485 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
/
Resource Hash
46f2212adc3d46f1cf1c201e95361d29258a5bc2f0f6d1c550d4482d2030b04d
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
content-type
text/plain
sec-ch-ua-mobile
?0

Response headers

access-control-expose-headers
*
content-encoding
br
etag
W/"609-apL2839xlGdmK++22Uv8md5Tb2A"
age
40234
x-content-type-options
nosniff
x-jsd-version-type
version
alt-svc
h3=":443";ma=86400,h3-29=":443";ma=86400,h3-27=":443";ma=86400
x-cache
HIT, HIT
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
application/json; charset=utf-8
x-served-by
cache-fra-eddf8230081-FRA, cache-rtm-ehrd2290057-RTM
vary
Accept-Encoding
cache-control
public, max-age=604800, s-maxage=43200
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
content-length
806
x-jsd-version
1.0.2914
GET
H2
200
pbhid Show response
id.hadron.ad.gt/api/v1/ Frame A4C8
2 B
0
151ms
151ms
Fetch
application/json
2606:4700:10::6814:2396
Cloudflare
General
Full URL
https://id.hadron.ad.gt/api/v1/pbhid?partner_id=574&_it=prebid&t=1&src=id&domain=footyroom.co&us_privacy=1---
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2606:4700:10::6814:2396 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
44136fa355b3678a1146ad16f7e8649e94fb4fc21fe77e8310c060f61caaff8a

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
content-type
text/plain
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=604800
cf-cache-status
DYNAMIC
access-control-allow-credentials
true
access-control-allow-methods
HEAD,GET,POST,PUT,DELETE,OPTIONS
cf-ray
a3abdc1bceb30e48-AMS
access-control-allow-origin
*
content-length
2
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
application/json; charset=utf8
server
cloudflare
access-control-allow-headers
authorization,content-type
POST
H2
200
prebid Show response
id5-sync.com/api/config/ Frame A4C8
195 B
650 B
52ms
24ms
Fetch
application/json
135.125.170.108
OVH OVH SAS
General
Full URL
https://id5-sync.com/api/config/prebid
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
135.125.170.108 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
ns3270108.ip-135-125-170.eu
Software
/
Resource Hash
61407ce1df311cd5bcff27d026e281a184a2cffe8fa24c3a2758ed2f2624b317
Security Headers
Name Value
Strict-Transport-Security max-age=63072000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=63072000; includeSubDomains; preload
content-encoding
gzip
access-control-allow-credentials
true
access-control-allow-origin
https://footyroom.co
p3p
CP="CAO PSA OUR"
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
application/json;charset=UTF-8
vary
origin,access-control-request-method,access-control-request-headers,accept-encoding
GET
H2
200
rid Show response
match.adsrvr.org/track/ Frame A4C8
63 B
0
61ms
61ms
Fetch
application/json
52.223.40.198
Amazon.com
General
Full URL
https://match.adsrvr.org/track/rid?ttd_pid=9t8jzll&fmt=json
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
52.223.40.198 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
a6370ebea231e0c9a.awsglobalaccelerator.com
Software
Kestrel /
Resource Hash
eff5a4b24cdbdc1f0ce7c7619eef45d704bf196d6583499ce9d5e242dd57dfa9

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
content-type
text/plain
sec-ch-ua-mobile
?0

Response headers

cache-control
private
content-encoding
gzip
access-control-allow-credentials
true
expires
Wed, 14 Oct 2026 02:11:13 GMT
access-control-allow-origin
https://footyroom.co
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
application/json
vary
Origin,Accept-Encoding
server
Kestrel
access-control-allow-headers
Origin, X-Requested-With, Content-Type, Content-Length, Content-Encoding, Vary, Cache-Control, Accept, x-integration-type
GET
H2
200
pbhid Show response
id.hadron.ad.gt/api/v1/ Frame A4C8
2 B
0
151ms
151ms
Fetch
application/json
2606:4700:10::6814:2396
Cloudflare
General
Full URL
https://id.hadron.ad.gt/api/v1/pbhid?partner_id=574&_it=prebid&t=1&src=id&domain=footyroom.co&us_privacy=1---
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2606:4700:10::6814:2396 -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
44136fa355b3678a1146ad16f7e8649e94fb4fc21fe77e8310c060f61caaff8a

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
content-type
text/plain
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=604800
cf-cache-status
DYNAMIC
access-control-allow-credentials
true
access-control-allow-methods
HEAD,GET,POST,PUT,DELETE,OPTIONS
cf-ray
a3abdc1bceb30e48-AMS
access-control-allow-origin
*
content-length
2
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
application/json; charset=utf8
server
cloudflare
access-control-allow-headers
authorization,content-type
POST
H2
200
prebid Show response
id5-sync.com/api/config/ Frame A4C8
195 B
650 B
51ms
25ms
Fetch
application/json
135.125.170.108
OVH OVH SAS
General
Full URL
https://id5-sync.com/api/config/prebid
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
135.125.170.108 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
ns3270108.ip-135-125-170.eu
Software
/
Resource Hash
61407ce1df311cd5bcff27d026e281a184a2cffe8fa24c3a2758ed2f2624b317
Security Headers
Name Value
Strict-Transport-Security max-age=63072000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=63072000; includeSubDomains; preload
content-encoding
gzip
access-control-allow-credentials
true
access-control-allow-origin
https://footyroom.co
p3p
CP="CAO PSA OUR"
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
application/json;charset=UTF-8
vary
origin,access-control-request-method,access-control-request-headers,accept-encoding
GET
H2
200
rid Show response
match.adsrvr.org/track/ Frame A4C8
63 B
0
61ms
61ms
Fetch
application/json
52.223.40.198
Amazon.com
General
Full URL
https://match.adsrvr.org/track/rid?ttd_pid=9t8jzll&fmt=json
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
52.223.40.198 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
a6370ebea231e0c9a.awsglobalaccelerator.com
Software
Kestrel /
Resource Hash
eff5a4b24cdbdc1f0ce7c7619eef45d704bf196d6583499ce9d5e242dd57dfa9

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
content-type
text/plain
sec-ch-ua-mobile
?0

Response headers

cache-control
private
content-encoding
gzip
access-control-allow-credentials
true
expires
Wed, 14 Oct 2026 02:11:13 GMT
access-control-allow-origin
https://footyroom.co
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
application/json
vary
Origin,Accept-Encoding
server
Kestrel
access-control-allow-headers
Origin, X-Requested-With, Content-Type, Content-Length, Content-Encoding, Vary, Cache-Control, Accept, x-integration-type
POST
H2
204
ortb Show response
srv.scalibur.io/adserver/ Frame 14B4
0
210 B
59ms
57ms
XHR
text/plain
185.167.98.14
CloudWebManage-EU...
General
Full URL
https://srv.scalibur.io/adserver/ortb?type=unit&cb=1789351873854_lc5oc1
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/adunit?id=56&width=300&height=169&url=https%3A%2F%2Ffootyroom.co%2Fmatches%2F80034717%2Fmanchester-united-vs-sabah-fk%2Freview&sids=%7B%7D&schain=1.0%2C1!nitropay.com%2C1728%2C1%2C%2C%2C&containerId=Nitro%20Desktop%20Video%20Ad-isolated&isDebug=0&cb=1789351873339_1cdfuw&us_privacy=1---&keyValues=%7B%22gamAdUnitId%22%3A%22%2F308365556%2C22913055933%2Fnitro-banner%2Fnitro-banner-2321%22%2C%22ttdPubId%22%3A%221728%22%2C%22siteId%22%3A%222321%22%2C%22nitro_gpid%22%3A%22Nitro%20Desktop%20Video%20Ad%22%7D
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
185.167.98.14 Amsterdam, Netherlands, ASN41436 (CloudWebManage-EU Kamatera Inc, US),
Reverse DNS
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
no-cache, no-store, must-revalidate
pragma
no-cache
age
0
access-control-allow-credentials
true
expires
0
access-control-allow-origin
https://footyroom.co
date
Mon, 14 Sep 2026 02:11:13 GMT
GET
H3
200
omweb-v1.js Show response
pagead2.googlesyndication.com/omsdk/releases/live/ Frame 2E93
48 KB
0
14ms
14ms
Script
text/javascript
142.251.20.154
Google LLC
General
Full URL
https://pagead2.googlesyndication.com/omsdk/releases/live/omweb-v1.js
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.20.154 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bx-in-f154.1e100.net
Software
sffe /
Resource Hash
6edb5275ff2227bece0bf3341bdabb6f2f6d8ff1fb31d726d263eb317996f4b3
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
age
535
report-to
{"group":"omsdk-team-release-policy","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/omsdk-team-release-policy"}]}
x-content-type-options
nosniff
expires
Mon, 14 Sep 2026 03:02:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:02:18 GMT
last-modified
Tue, 01 Sep 2026 17:39:54 GMT
content-type
text/javascript
vary
Accept-Encoding
cache-control
public, max-age=3600
cross-origin-opener-policy
same-origin; report-to="omsdk-team-release-policy"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/omsdk-team-release-policy
accept-ranges
bytes
content-length
17052
x-xss-protection
0
server
sffe
POST
H3
204
AGSKWxXcIhhbiu358SLpLSZn6QOYaPbwlxav7jRknBPngNDhiu-aHpWWnD2iRf3rbMleS48-7r4S1XoPT6c4gZz2exbyv7UHl-eY0YIPBUvEy2yfJ-HmYY3As4TrqkAoX_Vlr7ImJsCCaQ== Show response
fundingchoicesmessages.google.com/el/
0
28 B
60ms
52ms
XHR
text/html
142.251.110.100
Google LLC
General
Full URL
https://fundingchoicesmessages.google.com/el/AGSKWxXcIhhbiu358SLpLSZn6QOYaPbwlxav7jRknBPngNDhiu-aHpWWnD2iRf3rbMleS48-7r4S1XoPT6c4gZz2exbyv7UHl-eY0YIPBUvEy2yfJ-HmYY3As4TrqkAoX_Vlr7ImJsCCaQ==
Requested by
Host:
URL: /_/mss/boq-content-ads-contributor/_/js/k=boq-content-ads-contributor.ContributorServingResponseClientJs.nl.vyMVZXSm2Sw.es5.O/d=1/rs=AJlcJMwT-z7-Ua2kRQtmTjsz1eye77FxMQ/m=kernel_loader,loader_js_executable
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.110.100 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f100.1e100.net
Software
ESF /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Content-Security-Policy script-src 'report-sample' 'nonce-bueuudze5_diRyda51cvxg' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/ContributorLoggingHttp/cspreport;worker-src 'self', script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/ContributorLoggingHttp/cspreport/allowlist, require-trusted-types-for 'script';report-uri /_/ContributorLoggingHttp/cspreport
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
text/plain
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
86400
access-control-allow-methods
POST, GET, OPTIONS
x-content-type-options
nosniff
expires
Mon, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
text/html; charset=utf-8
x-frame-options
SAMEORIGIN
reporting-endpoints
default="/_/ContributorLoggingHttp/web-reports?context=eJzj0tDikmLw15Bi-FB_mfUHEC-cFsi2EohFDILYZIA47WA4Wx4QC_FwHFw_9yqbwIF5R1cyK7kk5RfGJ-fnlaTmlegmphTrgthFmUmlJflFKOzUMpCKnPz09My89HgjAyMzA0sDSz1Dg_gCAwDUWyws"
content-security-policy
script-src 'report-sample' 'nonce-bueuudze5_diRyda51cvxg' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/ContributorLoggingHttp/cspreport;worker-src 'self', script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/ContributorLoggingHttp/cspreport/allowlist, require-trusted-types-for 'script';report-uri /_/ContributorLoggingHttp/cspreport
cache-control
no-cache, no-store, max-age=0, must-revalidate
cross-origin-opener-policy
same-origin
pragma
no-cache
accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
access-control-allow-credentials
true
permissions-policy
ch-ua-arch=*, ch-ua-bitness=*, ch-ua-full-version=*, ch-ua-full-version-list=*, ch-ua-model=*, ch-ua-wow64=*, ch-ua-form-factors=*, ch-ua-platform=*, ch-ua-platform-version=*
access-control-allow-origin
https://footyroom.co
content-length
0
x-xss-protection
0
server
ESF
POST
H3
204
AGSKWxXcIhhbiu358SLpLSZn6QOYaPbwlxav7jRknBPngNDhiu-aHpWWnD2iRf3rbMleS48-7r4S1XoPT6c4gZz2exbyv7UHl-eY0YIPBUvEy2yfJ-HmYY3As4TrqkAoX_Vlr7ImJsCCaQ== Show response
fundingchoicesmessages.google.com/el/
0
28 B
93ms
86ms
XHR
text/html
142.251.110.100
Google LLC
General
Full URL
https://fundingchoicesmessages.google.com/el/AGSKWxXcIhhbiu358SLpLSZn6QOYaPbwlxav7jRknBPngNDhiu-aHpWWnD2iRf3rbMleS48-7r4S1XoPT6c4gZz2exbyv7UHl-eY0YIPBUvEy2yfJ-HmYY3As4TrqkAoX_Vlr7ImJsCCaQ==
Requested by
Host:
URL: /_/mss/boq-content-ads-contributor/_/js/k=boq-content-ads-contributor.ContributorServingResponseClientJs.nl.vyMVZXSm2Sw.es5.O/d=1/rs=AJlcJMwT-z7-Ua2kRQtmTjsz1eye77FxMQ/m=kernel_loader,loader_js_executable
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.110.100 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f100.1e100.net
Software
ESF /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script';report-uri /_/ContributorLoggingHttp/cspreport, script-src 'report-sample' 'nonce-rhRiXqjPqMKCCQaD_ReDig' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/ContributorLoggingHttp/cspreport;worker-src 'self', script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/ContributorLoggingHttp/cspreport/allowlist
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
text/plain
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
86400
access-control-allow-methods
POST, GET, OPTIONS
x-content-type-options
nosniff
expires
Mon, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
text/html; charset=utf-8
x-frame-options
SAMEORIGIN
reporting-endpoints
default="/_/ContributorLoggingHttp/web-reports?context=eJzj0tDikmLw05Bi-FB_mfUHEC-cFsi2EohFDILYZIA47WA4Wx4QC_FwHFw_9yqbwIze5buZlVyS8gvjk_PzSlLzSnQTU4p1QeyizKTSkvwiFHZqGUhFTn56emZeeryRgZGZgaWBpZ6hQXyBAQC_wyvm"
content-security-policy
require-trusted-types-for 'script';report-uri /_/ContributorLoggingHttp/cspreport, script-src 'report-sample' 'nonce-rhRiXqjPqMKCCQaD_ReDig' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/ContributorLoggingHttp/cspreport;worker-src 'self', script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/ContributorLoggingHttp/cspreport/allowlist
cache-control
no-cache, no-store, max-age=0, must-revalidate
cross-origin-opener-policy
same-origin
pragma
no-cache
accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
access-control-allow-credentials
true
permissions-policy
ch-ua-arch=*, ch-ua-bitness=*, ch-ua-full-version=*, ch-ua-full-version-list=*, ch-ua-model=*, ch-ua-wow64=*, ch-ua-form-factors=*, ch-ua-platform=*, ch-ua-platform-version=*
access-control-allow-origin
https://footyroom.co
content-length
0
x-xss-protection
0
server
ESF
GET
H3
200
AGSKWxUnOBBW-hvbA9ErthsSeIvOOMJlkyQSvymUxPJyPHo41tPtqEfDxG4ZPijk2IHMC95ksckL_TLd6KcimWJasheSnEntff6QyjTR02Ow1t5QHKLKK5GwnmFl7VCQ1OUa5l_ZB9V67w== Show response
fundingchoicesmessages.google.com/f/
5 KB
2 KB
64ms
60ms
Script
application/javascript
142.251.110.100
Google LLC
General
Full URL
https://fundingchoicesmessages.google.com/f/AGSKWxUnOBBW-hvbA9ErthsSeIvOOMJlkyQSvymUxPJyPHo41tPtqEfDxG4ZPijk2IHMC95ksckL_TLd6KcimWJasheSnEntff6QyjTR02Ow1t5QHKLKK5GwnmFl7VCQ1OUa5l_ZB9V67w==?fccs=W251bGwsbnVsbCxudWxsLG51bGwsbnVsbCxudWxsLFsxNzg5MzUxODczLDg2NjAwMDAwMF0sbnVsbCxudWxsLG51bGwsW251bGwsWzcsNl0sbnVsbCxudWxsLG51bGwsbnVsbCxudWxsLG51bGwsbnVsbCxudWxsLG51bGwsMV0sImh0dHBzOi8vZm9vdHlyb29tLmNvL21hdGNoZXMvODAwMzQ3MTcvbWFuY2hlc3Rlci11bml0ZWQtdnMtc2FiYWgtZmsvcmV2aWV3IixudWxsLFtbOCwidnlNVlpYU20yU3ciXSxbOSwibmwiXSxbMzUsIjE3ODkzNTE4NzIiXSxbMTksIjIiXSxbMjQsIiJdLFsyOSwiZmFsc2UiXV1d
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.110.100 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f100.1e100.net
Software
ESF /
Resource Hash
15b0bf6a136be84146f328db0a1d9af813441d63f2910f1296a7eebbabd10033
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script';report-uri /_/ContributorServingWebSwitchboardHttp/cspreport, script-src 'report-sample' 'nonce-DIKYmhP4ZI1yq5jsCsofkQ' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/ContributorServingWebSwitchboardHttp/cspreport;worker-src 'self', script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/ContributorServingWebSwitchboardHttp/cspreport/allowlist
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-content-type-options
nosniff
expires
Mon, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
application/javascript; charset=utf-8
x-frame-options
SAMEORIGIN
reporting-endpoints
default="/_/ContributorServingWebSwitchboardHttp/web-reports?context=eJzjStHikmJw05BiaL15jnU6EJcsOs_aBsRdQDwHiA0VLrE6A_GH-susP4C4SOIKawsQf6q6wSpSfYP1W7EvG0eJLxvLW3-2hdMC2VYCsYhBEJsMEKcdDGfLA2IhHo6D6-deZRPYMf3GWmYljaT8wvjk_LySosyk0pL8orTktNTi1KKy1KJ4IwMjMwNLA0s9Q8P4AgMA4sE6yw"
content-security-policy
require-trusted-types-for 'script';report-uri /_/ContributorServingWebSwitchboardHttp/cspreport, script-src 'report-sample' 'nonce-DIKYmhP4ZI1yq5jsCsofkQ' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/ContributorServingWebSwitchboardHttp/cspreport;worker-src 'self', script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/ContributorServingWebSwitchboardHttp/cspreport/allowlist
cache-control
no-cache, no-store, max-age=0, must-revalidate
timing-allow-origin
*
cross-origin-opener-policy
same-origin
pragma
no-cache
accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
cross-origin-resource-policy
cross-origin
permissions-policy
ch-ua-arch=*, ch-ua-bitness=*, ch-ua-full-version=*, ch-ua-full-version-list=*, ch-ua-model=*, ch-ua-wow64=*, ch-ua-form-factors=*, ch-ua-platform=*, ch-ua-platform-version=*
x-xss-protection
0
server
ESF
POST
H2
204
collect
analytics.google.com/g/
0
0
76ms
22ms
Fetch
text/plain
2001:4860:4802:36::181
Google LLC
General
Full URL
https://analytics.google.com/g/collect?v=2&tid=G-CGXL08N85B&gtm=45je6992v9116169481za20g&_p=1789351872040&_gaz=1&gcd=13l3l3l3l2l1&npa=0&dma=0&tcfd=1000g&ecid=240706014&_eu=ABAIAGA&cid=1302944229.1789351873&frm=0&pscdl=noapi&rcb=18&sr=1600x1200&uaa=x86&uab=64&uafvl=Chromium%3B153.0.0.0%7CGoogle%2520Chrome%3B153.0.0.0%7CNot_A%2520Brand%3B8.0.0.0&uam=&uamb=0&uap=Linux&uapv=&uaw=0&ul=nl-nl&gaf=2&_s=1&tag_exp=115938465~115938469~118897920~118897930~120213116~120385423~120469145~120469153&dl=https%3A%2F%2Ffootyroom.co%2Fmatches%2F80034717%2Fmanchester-united-vs-sabah-fk%2Freview&dt=Manchester%20United%204-0%20Sabah%20FK%20Highlights%2C%20Goals%20%26%20Key%20Moments%20(10%20Sep%202026)%20%7C%20Champions%20League%20-%20FootyRoom&sid=1789351873&sct=1&seg=0&en=page_view&_fv=1&_ss=1&_ee=1&ep.ua_dimension_1=0&tfd=3183
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtag/js?id=G-CGXL08N85B&cx=c&_slc=1
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:4802:36::181 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
Golfe2 /
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, no-store, must-revalidate
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
content-security-policy-report-only
script-src 'none'; form-action 'none'; frame-src 'none'; report-uri https://csp.withgoogle.com/csp/scaffolding/ascnsrsggc:197:0
report-to
{"group":"ascnsrsggc:197:0","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/scaffolding/ascnsrsggc:197:0"}],}
expires
Fri, 01 Jan 1990 00:00:00 GMT
access-control-allow-origin
https://footyroom.co
cross-origin-opener-policy-report-only
same-origin; report-to=ascnsrsggc:197:0
content-length
0
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
text/plain
server
Golfe2
POST
H2
204
collect
stats.g.doubleclick.net/g/
0
546 B
139ms
47ms
Ping
text/plain
2a00:1450:4001:c21::9a
Google LLC
General
Full URL
https://stats.g.doubleclick.net/g/collect?v=2&tid=G-CGXL08N85B&cid=1302944229.1789351873&gtm=45je6992v9116169481za20g&rcb=18&aip=1&dma=0&gcd=13l3l3l3l2l1&npa=0&frm=0&tag_exp=115938465~115938469~118897920~118897930~120213116~120385423~120469145~120469153
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtag/js?id=G-CGXL08N85B&cx=c&_slc=1
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a00:1450:4001:c21::9a Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
Golfe2 /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, no-store, must-revalidate
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
content-security-policy-report-only
script-src 'none'; form-action 'none'; frame-src 'none'; report-uri https://csp.withgoogle.com/csp/scaffolding/ascnsrsggc:165:0
report-to
{"group":"ascnsrsggc:165:0","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/scaffolding/ascnsrsggc:165:0"}],}
expires
Fri, 01 Jan 1990 00:00:00 GMT
access-control-allow-origin
https://footyroom.co
cross-origin-opener-policy-report-only
same-origin; report-to=ascnsrsggc:165:0
content-length
0
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
text/plain
server
Golfe2
GET
H2
200
v1 Show response
lb.eu-1-id5-sync.com/lb/ Frame 22B1
45 B
331 B
77ms
22ms
Fetch
application/json
135.125.170.28
OVH OVH SAS
General
Full URL
https://lb.eu-1-id5-sync.com/lb/v1
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
135.125.170.28 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
ns31872155.ip-135-125-170.eu
Software
/
Resource Hash
007d02e9c6729b59d21f2400bf2e4bd98a637be339b583ca58f418013909fe54
Security Headers
Name Value
Strict-Transport-Security max-age=63072000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=63072000; includeSubDomains; preload
access-control-allow-origin
https://footyroom.co
content-encoding
gzip
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
application/json;charset=UTF-8
vary
origin,access-control-request-method,access-control-request-headers,accept-encoding
GET
H2
200
v1 Show response
lb.eu-1-id5-sync.com/lb/ Frame A4C8
45 B
330 B
91ms
21ms
Fetch
application/json
135.125.170.28
OVH OVH SAS
General
Full URL
https://lb.eu-1-id5-sync.com/lb/v1
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
135.125.170.28 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
ns31872155.ip-135-125-170.eu
Software
/
Resource Hash
83ecca4db46f0b53049489868d70337081985ba5557d42bd397609e7d59bfcc9
Security Headers
Name Value
Strict-Transport-Security max-age=63072000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=63072000; includeSubDomains; preload
access-control-allow-origin
https://footyroom.co
content-encoding
gzip
date
Mon, 14 Sep 2026 02:11:14 GMT
content-type
application/json;charset=UTF-8
vary
origin,access-control-request-method,access-control-request-headers,accept-encoding
GET
H2
200
v1 Show response
lb.eu-1-id5-sync.com/lb/ Frame A4C8
45 B
330 B
115ms
23ms
Fetch
application/json
135.125.170.28
OVH OVH SAS
General
Full URL
https://lb.eu-1-id5-sync.com/lb/v1
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
135.125.170.28 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
ns31872155.ip-135-125-170.eu
Software
/
Resource Hash
825929ab83c989bfbfcbcfa47d0bab1eeea39bb18436294ed531fbd252038abc
Security Headers
Name Value
Strict-Transport-Security max-age=63072000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=63072000; includeSubDomains; preload
access-control-allow-origin
https://footyroom.co
content-encoding
gzip
date
Mon, 14 Sep 2026 02:11:14 GMT
content-type
application/json;charset=UTF-8
vary
origin,access-control-request-method,access-control-request-headers,accept-encoding
GET
H2
200
v1 Show response
lb.eu-1-id5-sync.com/lb/ Frame 22B1
45 B
330 B
139ms
23ms
Fetch
application/json
135.125.170.28
OVH OVH SAS
General
Full URL
https://lb.eu-1-id5-sync.com/lb/v1
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
135.125.170.28 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
ns31872155.ip-135-125-170.eu
Software
/
Resource Hash
ffcffbf74e967c947fe558fc18e1e185f9528c93cf7ca606583b9e7dd2f19bcc
Security Headers
Name Value
Strict-Transport-Security max-age=63072000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=63072000; includeSubDomains; preload
access-control-allow-origin
https://footyroom.co
content-encoding
gzip
date
Mon, 14 Sep 2026 02:11:14 GMT
content-type
application/json;charset=UTF-8
vary
origin,access-control-request-method,access-control-request-headers,accept-encoding
GET
H3
200
AGSKWxXBcfXXVXfngNJGV459A68yzwEij7M2uuWvqIk96cDUd19H0Zn3BnrKGogvKsay2qsRkt1-F3KpNuvGZtMJQ21g0Ap9TYHaWOnnZC777GYWX-v0t1N_i1njYSSIS8eZdShOSucVww== Show response
fundingchoicesmessages.google.com/f/
2 KB
1 KB
66ms
66ms
Script
application/javascript
142.251.110.100
Google LLC
General
Full URL
https://fundingchoicesmessages.google.com/f/AGSKWxXBcfXXVXfngNJGV459A68yzwEij7M2uuWvqIk96cDUd19H0Zn3BnrKGogvKsay2qsRkt1-F3KpNuvGZtMJQ21g0Ap9TYHaWOnnZC777GYWX-v0t1N_i1njYSSIS8eZdShOSucVww==?fccs=W251bGwsbnVsbCxudWxsLG51bGwsbnVsbCxudWxsLFsxNzg5MzUxODczLDkzOTAwMDAwMF0sbnVsbCxudWxsLG51bGwsW251bGwsWzcsNiwxMF0sbnVsbCxudWxsLG51bGwsbnVsbCxudWxsLG51bGwsbnVsbCxudWxsLG51bGwsMV0sImh0dHBzOi8vZm9vdHlyb29tLmNvL21hdGNoZXMvODAwMzQ3MTcvbWFuY2hlc3Rlci11bml0ZWQtdnMtc2FiYWgtZmsvcmV2aWV3IixudWxsLFtbOCwidnlNVlpYU20yU3ciXSxbOSwibmwiXSxbMzUsIjE3ODkzNTE4NzIiXSxbMTksIjIiXSxbMjQsIiJdLFsyOSwiZmFsc2UiXV1d
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.110.100 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f100.1e100.net
Software
ESF /
Resource Hash
edff9075e321b40bdc5088b710519747dff0d355e2267be8fd12ffb956d03847
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script';report-uri /_/ContributorServingWebSwitchboardHttp/cspreport, script-src 'report-sample' 'nonce-ANivqE10ozGE27R88rjsCQ' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/ContributorServingWebSwitchboardHttp/cspreport;worker-src 'self', script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/ContributorServingWebSwitchboardHttp/cspreport/allowlist
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-content-type-options
nosniff
expires
Mon, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
application/javascript; charset=utf-8
x-frame-options
SAMEORIGIN
reporting-endpoints
default="/_/ContributorServingWebSwitchboardHttp/web-reports?context=eJzjStHikmLw0JBiaL15jnU6EJcsOs_aBsRdQDwHiA0VLrE6A_GH-susP4C4SOIKawsQf6q6wSpSfYP1W7EvG0eJLxvLW3-2hdMC2VYCsYhBEJsMEKcdDGfLA2IhHo6D6-deZRPYcHHRBWYljaT8wvjk_LySosyk0pL8orTktNTi1KKy1KJ4IwMjMwNLA0s9Q8P4AgMA6Ws67A"
content-security-policy
require-trusted-types-for 'script';report-uri /_/ContributorServingWebSwitchboardHttp/cspreport, script-src 'report-sample' 'nonce-ANivqE10ozGE27R88rjsCQ' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/ContributorServingWebSwitchboardHttp/cspreport;worker-src 'self', script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/ContributorServingWebSwitchboardHttp/cspreport/allowlist
cache-control
no-cache, no-store, max-age=0, must-revalidate
timing-allow-origin
*
cross-origin-opener-policy
same-origin
pragma
no-cache
accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
cross-origin-resource-policy
cross-origin
permissions-policy
ch-ua-arch=*, ch-ua-bitness=*, ch-ua-full-version=*, ch-ua-full-version-list=*, ch-ua-model=*, ch-ua-wow64=*, ch-ua-form-factors=*, ch-ua-platform=*, ch-ua-platform-version=*
x-xss-protection
0
server
ESF
POST
H2
200
1858.json Show response
id5-sync.com/g/v2/ Frame 22B1
513 B
768 B
24ms
22ms
Fetch
application/json
135.125.170.108
OVH OVH SAS
General
Full URL
https://id5-sync.com/g/v2/1858.json
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
135.125.170.108 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
ns3270108.ip-135-125-170.eu
Software
/
Resource Hash
52627dfef9258889938f55063996e3ff713dd22756730d5ef4418622587f1b3a
Security Headers
Name Value
Strict-Transport-Security max-age=63072000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=63072000; includeSubDomains; preload
access-control-allow-origin
https://footyroom.co
date
Mon, 14 Sep 2026 02:11:14 GMT
content-type
application/json
vary
Origin, Access-Control-Request-Method, Access-Control-Request-Headers
access-control-allow-credentials
true
POST
H3
204
AGSKWxUW2meqw6VM7OFliCtlR6xjlSroSZq-0K9kU-JkfyhOq68kQG4spXAllQFJUbgknK5FOIPNvPA95fprFFbhkRIPsDEwKkLz5NXmw5l--P0BstIMci4-wQqyyMdwcjHtvvYy_dXXvA== Show response
fundingchoicesmessages.google.com/el/
0
28 B
120ms
119ms
XHR
text/html
142.251.110.100
Google LLC
General
Full URL
https://fundingchoicesmessages.google.com/el/AGSKWxUW2meqw6VM7OFliCtlR6xjlSroSZq-0K9kU-JkfyhOq68kQG4spXAllQFJUbgknK5FOIPNvPA95fprFFbhkRIPsDEwKkLz5NXmw5l--P0BstIMci4-wQqyyMdwcjHtvvYy_dXXvA==
Requested by
Host:
URL: /_/mss/boq-content-ads-contributor/_/js/k=boq-content-ads-contributor.ContributorServingResponseClientJs.nl.vyMVZXSm2Sw.es5.O/d=1/rs=AJlcJMwT-z7-Ua2kRQtmTjsz1eye77FxMQ/m=kernel_loader,loader_js_executable
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.110.100 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f100.1e100.net
Software
ESF /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Content-Security-Policy script-src 'report-sample' 'nonce-xieOuEX1PoVBARb1oCUKHA' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/ContributorLoggingHttp/cspreport;worker-src 'self', script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/ContributorLoggingHttp/cspreport/allowlist, require-trusted-types-for 'script';report-uri /_/ContributorLoggingHttp/cspreport
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
text/plain
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
86400
access-control-allow-methods
POST, GET, OPTIONS
x-content-type-options
nosniff
expires
Mon, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:14 GMT
content-type
text/html; charset=utf-8
x-frame-options
SAMEORIGIN
reporting-endpoints
default="/_/ContributorLoggingHttp/web-reports?context=eJzj0tDikmLw05Bi-FB_mfUHEC-cFsi2EohFDILYZIA47WA4Wx4QC3FzHFo_9yqbQEfPfx0ll6T8wvjk_LyS1LwS3cSUYl0QuygzqbQkvwiFnVoGUpGTn56emZceb2RgZGZgaWCpZ2gQX2AAAJhaK5s"
content-security-policy
script-src 'report-sample' 'nonce-xieOuEX1PoVBARb1oCUKHA' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/ContributorLoggingHttp/cspreport;worker-src 'self', script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/ContributorLoggingHttp/cspreport/allowlist, require-trusted-types-for 'script';report-uri /_/ContributorLoggingHttp/cspreport
cache-control
no-cache, no-store, max-age=0, must-revalidate
cross-origin-opener-policy
same-origin
pragma
no-cache
accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
access-control-allow-credentials
true
permissions-policy
ch-ua-arch=*, ch-ua-bitness=*, ch-ua-full-version=*, ch-ua-full-version-list=*, ch-ua-model=*, ch-ua-wow64=*, ch-ua-form-factors=*, ch-ua-platform=*, ch-ua-platform-version=*
access-control-allow-origin
https://footyroom.co
content-length
0
x-xss-protection
0
server
ESF
GET
H3
200
AGSKWxUgX9ZUDLWF-8n7vUa-ZAhs0uCh9Kd_aSBkmADr9QkINW_BRQQ8gGpSZ2a0UXTtl9OgVYFqulj7kTuqleoMIIkUeLZwhWFBpuVs5szEglCIDltpG_aUf_T2j0Fn9pbN8KKoNv-htg== Show response
fundingchoicesmessages.google.com/f/
3 KB
2 KB
66ms
66ms
Script
application/javascript
142.251.110.100
Google LLC
General
Full URL
https://fundingchoicesmessages.google.com/f/AGSKWxUgX9ZUDLWF-8n7vUa-ZAhs0uCh9Kd_aSBkmADr9QkINW_BRQQ8gGpSZ2a0UXTtl9OgVYFqulj7kTuqleoMIIkUeLZwhWFBpuVs5szEglCIDltpG_aUf_T2j0Fn9pbN8KKoNv-htg==?fccs=W251bGwsbnVsbCxudWxsLG51bGwsbnVsbCxudWxsLFsxNzg5MzUxODc0LDEwMDAwMDAwXSxudWxsLG51bGwsbnVsbCxbbnVsbCxbNyw2LDEwLDldLG51bGwsMixudWxsLCJlbiIsbnVsbCxudWxsLG51bGwsbnVsbCxudWxsLDFdLCJodHRwczovL2Zvb3R5cm9vbS5jby9tYXRjaGVzLzgwMDM0NzE3L21hbmNoZXN0ZXItdW5pdGVkLXZzLXNhYmFoLWZrL3JldmlldyIsbnVsbCxbWzgsInZ5TVZaWFNtMlN3Il0sWzksIm5sIl0sWzM1LCIxNzg5MzUxODcyIl0sWzE5LCIyIl0sWzI0LCIiXSxbMjksImZhbHNlIl1dXQ
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.110.100 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f100.1e100.net
Software
ESF /
Resource Hash
a31ae035f391740bef8c134ff847e1e5de9bd8fe998ede383df0e5374f007474
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script';report-uri /_/ContributorServingWebSwitchboardHttp/cspreport, script-src 'report-sample' 'nonce-3c3-pNVMOO5pVo77koHWIQ' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/ContributorServingWebSwitchboardHttp/cspreport;worker-src 'self', script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/ContributorServingWebSwitchboardHttp/cspreport/allowlist
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-content-type-options
nosniff
expires
Mon, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:14 GMT
content-type
application/javascript; charset=utf-8
x-frame-options
SAMEORIGIN
reporting-endpoints
default="/_/ContributorServingWebSwitchboardHttp/web-reports?context=eJzjytHikmLw1JBiOHHrNtMFIG69eY51OhCXLDrP2gbEXUA8B4gNFS6xOgPxh_rLrD-AuEjiCmsLEH-qusEqUn2D9VuxLxtHiS8by1t_toXTAtlWArGIQRCbDBCnHQxnywNiIW6OQ-vnXmUT2LD3irCSRlJ-YXxyfl5JUWZSaUl-UVpyWmpxalFZalG8kYGRmYGlgaWeoWF8gQEArS0_WQ"
content-security-policy
require-trusted-types-for 'script';report-uri /_/ContributorServingWebSwitchboardHttp/cspreport, script-src 'report-sample' 'nonce-3c3-pNVMOO5pVo77koHWIQ' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/ContributorServingWebSwitchboardHttp/cspreport;worker-src 'self', script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/ContributorServingWebSwitchboardHttp/cspreport/allowlist
cache-control
no-cache, no-store, max-age=0, must-revalidate
timing-allow-origin
*
cross-origin-opener-policy
same-origin
pragma
no-cache
accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
cross-origin-resource-policy
cross-origin
permissions-policy
ch-ua-arch=*, ch-ua-bitness=*, ch-ua-full-version=*, ch-ua-full-version-list=*, ch-ua-model=*, ch-ua-wow64=*, ch-ua-form-factors=*, ch-ua-platform=*, ch-ua-platform-version=*
x-xss-protection
0
server
ESF
POST
H2
200
1858.json Show response
id5-sync.com/g/v2/ Frame A4C8
512 B
767 B
24ms
22ms
Fetch
application/json
135.125.170.108
OVH OVH SAS
General
Full URL
https://id5-sync.com/g/v2/1858.json
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
135.125.170.108 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
ns3270108.ip-135-125-170.eu
Software
/
Resource Hash
c667d1bd3d6cd0c69087f6df772bbe12837dec773e1b1a1999618c3537c2fb7b
Security Headers
Name Value
Strict-Transport-Security max-age=63072000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=63072000; includeSubDomains; preload
access-control-allow-origin
https://footyroom.co
date
Mon, 14 Sep 2026 02:11:14 GMT
content-type
application/json
vary
Origin, Access-Control-Request-Method, Access-Control-Request-Headers
access-control-allow-credentials
true
POST
H2
200
1858.json Show response
id5-sync.com/g/v2/ Frame A4C8
512 B
767 B
23ms
23ms
Fetch
application/json
135.125.170.108
OVH OVH SAS
General
Full URL
https://id5-sync.com/g/v2/1858.json
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
135.125.170.108 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
ns3270108.ip-135-125-170.eu
Software
/
Resource Hash
d3f37669da130981cc76d2dcefb22a38de82ee6e0fb105b07facebcd7f4eddbc
Security Headers
Name Value
Strict-Transport-Security max-age=63072000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=63072000; includeSubDomains; preload
access-control-allow-origin
https://footyroom.co
date
Mon, 14 Sep 2026 02:11:14 GMT
content-type
application/json
vary
Origin, Access-Control-Request-Method, Access-Control-Request-Headers
access-control-allow-credentials
true
POST
H2
200
1858.json Show response
id5-sync.com/g/v2/ Frame 22B1
513 B
768 B
25ms
24ms
Fetch
application/json
135.125.170.108
OVH OVH SAS
General
Full URL
https://id5-sync.com/g/v2/1858.json
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
135.125.170.108 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
ns3270108.ip-135-125-170.eu
Software
/
Resource Hash
f105d3d584b05d6d793ab6a36fb095095939320f95c68802513f46638cb5783d
Security Headers
Name Value
Strict-Transport-Security max-age=63072000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=63072000; includeSubDomains; preload
access-control-allow-origin
https://footyroom.co
date
Mon, 14 Sep 2026 02:11:14 GMT
content-type
application/json
vary
Origin, Access-Control-Request-Method, Access-Control-Request-Headers
access-control-allow-credentials
true
POST
H2
204
v1 Show response
btlr.sharethrough.com/universal/ Frame A4C8
0
119 B
88ms
22ms
Fetch
63.180.245.66
Amazon.com
General
Full URL
https://btlr.sharethrough.com/universal/v1?supply_id=WYu2BXv1
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
63.180.245.66 Frankfurt am Main, Germany, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-63-180-245-66.eu-central-1.compute.amazonaws.com
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=16000000; includeSubDomains; preload;

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
content-type
text/plain
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=16000000; includeSubDomains; preload;
access-control-allow-origin
https://footyroom.co
access-control-allow-credentials
true
POST
H2
200
Nitro Show response
direct.adsrvr.org/bid/bidder/ Frame A4C8
0
244 B
119ms
32ms
Fetch
application/json
52.223.6.21
Amazon.com
General
Full URL
https://direct.adsrvr.org/bid/bidder/Nitro
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
52.223.6.21 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
a8c33d2b6751b365d.awsglobalaccelerator.com
Software
Kestrel /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
content-type
text/plain
sec-ch-ua-mobile
?0

Response headers

x-openrtb-version
2.3
cache-control
private
access-control-allow-credentials
true
access-control-allow-origin
https://footyroom.co
content-length
0
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
application/json
server
Kestrel
access-control-allow-headers
Origin, X-Requested-With, Content-Type, Content-Length, Content-Encoding, Vary, Cache-Control, Accept, x-integration-type
POST
H2
204
prebid Show response
prebid.media.net/rtb/ Frame A4C8
0
422 B
82ms
35ms
Fetch
34.36.209.34
Google LLC
General
Full URL
https://prebid.media.net/rtb/prebid?cid=8CU87559X
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.36.209.34 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
34.209.36.34.bc.googleusercontent.com
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
content-type
text/plain
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=0, no-cache, no-store, must-revalidate
pragma
no-cache
accept-ch
Sec-CH-UA-Mobile,Sec-CH-UA-Platform,Sec-CH-UA-Platform-Version,Sec-CH-UA-Arch,Sec-CH-UA-Bitness,Sec-CH-UA-Full-Version-List,Sec-CH-UA-Model
access-control-allow-credentials
true
via
1.1 google
expires
Mon, 14 Sep 2026 02:11:14 GMT
access-control-allow-origin
https://footyroom.co
alt-svc
h3=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:14 GMT
vary
Accept-Encoding
GET
H2
200
fastlane.json Show response
fastlane.rubiconproject.com/a/api/ Frame A4C8
354 B
560 B
96ms
36ms
Fetch
application/json
2602:803:c003:200::21
Magnite
General
Full URL
https://fastlane.rubiconproject.com/a/api/fastlane.json?account_id=17374&site_id=591076&zone_id=3774048&size_id=44&p_pos=atf&us_privacy=1---&rp_schain=1.0,1!nitropay.com,1728,1,,,&eid_id5-sync.com=0%5E1%5E%5E%5E%5E%5E&eid_pubcid.org=f9b61d32-b319-438f-ac42-44bf60dc1b64%5E1%5E%5E%5E%5E%5E&rf=https%3A%2F%2Ffootyroom.co%2Fmatches%2F80034717%2Fmanchester-united-vs-sabah-fk%2Freview&kw=football%2Csoccer%2Chighlights%2Cstatistics%2Cgoals%2Cvideo&tg_i.domain=footyroom.co&tg_i.page=https%3A%2F%2Ffootyroom.co%2Fmatches%2F80034717%2Fmanchester-united-vs-sabah-fk%2Freview&tk_flint=pbjs_lite_v9.53.3&x_source.tid=7e5e0087-2b4f-411c-829e-86a580e0451a&l_pb_bid_id=9352aa5f8849a8&p_screen_res=1600x1200&rp_secure=1&x_imp.ext.tid=f2a40a11-a9a4-4c0f-8f43-68ff96381803&rp_hard_floor=0.1&p_gpid=%2Fscl%2Fdisplay%2F56%2Ffootyroom.co&m_ch_ua=%22Chromium%22%7Cv%3D%22153%22%2C%22Google%20Chrome%22%7Cv%3D%22153%22%2C%22Not_A%20Brand%22%7Cv%3D%228%22&m_ch_mobile=%3F0&m_ch_platform=Linux&slots=1&rand=0.23332525164457418
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2602:803:c003:200::21 Amsterdam, Netherlands, ASN26667 (RUBICONPROJECT - Magnite, Inc., US),
Reverse DNS
Software
nginx/1.30.4 /
Resource Hash
ff591a993bfb2d313dd189d15d4a535fe09649178ea2b24620bb4c474be5ba87

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
content-type
text/plain
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, no-store, max-age=0, must-revalidate
pragma
no-cache
access-control-allow-credentials
true
expires
Wed, 17 Sep 1975 21:32:10 GMT
access-control-allow-origin
https://footyroom.co
content-length
354
date
Mon, 14 Sep 2026 02:11:14 GMT
content-type
application/json
vary
Accept-Encoding
server
nginx/1.30.4
POST
H2
200
unruly_prebid Show response
targeting.unrulymedia.com/ Frame A4C8
11 B
202 B
70ms
40ms
Fetch
application/json
46.228.165.115
Amobee NEXXEN GRO...
General
Full URL
https://targeting.unrulymedia.com/unruly_prebid
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
46.228.165.115 , United Kingdom, ASN56396 (Amobee NEXXEN GROUP LTD, GB),
Reverse DNS
Software
/
Resource Hash
846949c5a40e3ffbb702473e54dfac0646541aa624a844369b6e24e51ddaf96b

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
content-type
application/json
sec-ch-ua-mobile
?0

Response headers

access-control-allow-origin
https://footyroom.co
cache-control
private, max-age=0, no-cache, no-store
content-length
11
date
Mon, 14 Sep 2026 02:11:14 GMT
pragma
no-cache
content-type
application/json
access-control-allow-credentials
true
OPTIONS
H2
204
unruly_prebid
targeting.unrulymedia.com/ Frame
0
0
79ms
15ms
Preflight
text/plain
46.228.165.115
Amobee NEXXEN GRO...
General
Full URL
https://targeting.unrulymedia.com/unruly_prebid
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
46.228.165.115 , United Kingdom, ASN56396 (Amobee NEXXEN GROUP LTD, GB),
Reverse DNS
Software
/
Resource Hash

Request headers

Accept
*/*
Access-Control-Request-Headers
content-type
Access-Control-Request-Method
POST
Origin
https://footyroom.co
Sec-Fetch-Mode
cors
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36

Response headers

access-control-allow-credentials
true
access-control-allow-headers
DNT,X-CustomHeader,Keep-Alive,User-Agent,X-Requested-With,If-Modified-Since,Cache-Control,Content-Type,Accept-Encoding,Origin,Accept-Language,X-CSRF-Token,x-unruly-override
access-control-allow-methods
GET, POST, OPTIONS
access-control-allow-origin
https://footyroom.co
access-control-max-age
1728000
content-type
text/plain charset=UTF-8
date
Mon, 14 Sep 2026 02:11:14 GMT
POST
H2
204
hb-mm-multi Show response
hb.minutemedia-prebid.com/ Frame 22B1
0
90 B
161ms
40ms
Fetch
35.207.108.208
Google LLC
General
Full URL
https://hb.minutemedia-prebid.com/hb-mm-multi
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
35.207.108.208 Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
208.108.207.35.bc.googleusercontent.com
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
content-type
text/plain
sec-ch-ua-mobile
?0

Response headers

via
1.1 google
access-control-allow-origin
https://footyroom.co
date
Mon, 14 Sep 2026 02:11:14 GMT
access-control-allow-credentials
true
GET
H2
200
fastlane.json Show response
fastlane.rubiconproject.com/a/api/ Frame 22B1
379 B
413 B
45ms
45ms
Fetch
application/json
2602:803:c003:200::21
Magnite
General
Full URL
https://fastlane.rubiconproject.com/a/api/fastlane.json?account_id=17374&site_id=591076&zone_id=3774048&size_id=2&alt_size_ids=1%2C43%2C44%2C55&p_pos=atf&us_privacy=1---&rp_schain=1.0,1!nitropay.com,1728,1,,,&eid_id5-sync.com=0%5E1%5E%5E%5E%5E%5E&eid_pubcid.org=242313d3-e4ae-4089-9e15-14b0cb23c838%5E1%5E%5E%5E%5E%5E&rf=https%3A%2F%2Ffootyroom.co%2Fmatches%2F80034717%2Fmanchester-united-vs-sabah-fk%2Freview&kw=football%2Csoccer%2Chighlights%2Cstatistics%2Cgoals%2Cvideo&tg_i.domain=footyroom.co&tg_i.page=https%3A%2F%2Ffootyroom.co%2Fmatches%2F80034717%2Fmanchester-united-vs-sabah-fk%2Freview&tk_flint=pbjs_lite_v9.53.3&x_source.tid=52aaf226-2595-4656-b325-6a29d2bf81ee&l_pb_bid_id=57a70e703c56b6&p_screen_res=1600x1200&rp_secure=1&x_imp.ext.tid=b6e9daff-115d-4abe-8fcc-a48668966f7c&rp_hard_floor=0.1&p_gpid=%2Fscl%2Fdisplay%2F56%2Ffootyroom.co&m_ch_ua=%22Chromium%22%7Cv%3D%22153%22%2C%22Google%20Chrome%22%7Cv%3D%22153%22%2C%22Not_A%20Brand%22%7Cv%3D%228%22&m_ch_mobile=%3F0&m_ch_platform=Linux&slots=1&rand=0.03470215222894668
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2602:803:c003:200::21 Amsterdam, Netherlands, ASN26667 (RUBICONPROJECT - Magnite, Inc., US),
Reverse DNS
Software
nginx/1.30.4 /
Resource Hash
00f3330eef64aed5914fcd3154c47b91076257797ed9831cac13aa9e239df47a

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
content-type
text/plain
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, no-store, max-age=0, must-revalidate
pragma
no-cache
access-control-allow-credentials
true
expires
Wed, 17 Sep 1975 21:32:10 GMT
access-control-allow-origin
https://footyroom.co
content-length
379
date
Mon, 14 Sep 2026 02:11:14 GMT
content-type
application/json
vary
Accept-Encoding
server
nginx/1.30.4
POST

bid
ssb-global.smartadserver.com/api/ Frame 22B1
0
0


POST
H2
204
prebid Show response
prebid.media.net/rtb/ Frame 22B1
0
149 B
38ms
36ms
Fetch
34.36.209.34
Google LLC
General
Full URL
https://prebid.media.net/rtb/prebid?cid=8CU87559X
Requested by
Host: srv.scalibur.io
URL: https://srv.scalibur.io/adserver/static/prebid9.53.3-new.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.36.209.34 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
34.209.36.34.bc.googleusercontent.com
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
content-type
text/plain
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=0, no-cache, no-store, must-revalidate
pragma
no-cache
accept-ch
Sec-CH-UA-Mobile,Sec-CH-UA-Platform,Sec-CH-UA-Platform-Version,Sec-CH-UA-Arch,Sec-CH-UA-Bitness,Sec-CH-UA-Full-Version-List,Sec-CH-UA-Model
access-control-allow-credentials
true
via
1.1 google
expires
Mon, 14 Sep 2026 02:11:14 GMT
access-control-allow-origin
https://footyroom.co
alt-svc
h3=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:14 GMT
vary
Accept-Encoding
POST
H3
204
AGSKWxUArsg9KHcRF80kWHjYSCxIrdxL6s57q3OnpxXhUCdEsPmZBghOsVT_qNmqKnF2pA85piiGb0dxxpAcjvD8zu9XbQ2AFMyvEWj9JGzVwcISOLpTxmBumwWsw9SDedj5xNsy_3mHIw== Show response
fundingchoicesmessages.google.com/el/
0
28 B
50ms
49ms
XHR
text/html
142.251.110.100
Google LLC
General
Full URL
https://fundingchoicesmessages.google.com/el/AGSKWxUArsg9KHcRF80kWHjYSCxIrdxL6s57q3OnpxXhUCdEsPmZBghOsVT_qNmqKnF2pA85piiGb0dxxpAcjvD8zu9XbQ2AFMyvEWj9JGzVwcISOLpTxmBumwWsw9SDedj5xNsy_3mHIw==
Requested by
Host:
URL: /_/mss/boq-content-ads-contributor/_/js/k=boq-content-ads-contributor.ContributorServingResponseClientJs.nl.vyMVZXSm2Sw.es5.O/d=1/rs=AJlcJMwT-z7-Ua2kRQtmTjsz1eye77FxMQ/m=kernel_loader,loader_js_executable
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.110.100 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f100.1e100.net
Software
ESF /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Content-Security-Policy script-src 'report-sample' 'nonce-VC4jqRqKT3prRTADB6JRkg' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/ContributorLoggingHttp/cspreport;worker-src 'self', script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/ContributorLoggingHttp/cspreport/allowlist, require-trusted-types-for 'script';report-uri /_/ContributorLoggingHttp/cspreport
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
text/plain
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
86400
access-control-allow-methods
POST, GET, OPTIONS
x-content-type-options
nosniff
expires
Mon, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:14 GMT
content-type
text/html; charset=utf-8
x-frame-options
SAMEORIGIN
reporting-endpoints
default="/_/ContributorLoggingHttp/web-reports?context=eJzj0tDikmLw0pBi-FB_mfUHEC-cFsi2EohFDILYZIA47WA4Wx4QC3FzHFo_9yqbwITuwzVKLkn5hfHJ-XklqXkluokpxbogdlFmUmlJfhEKO7UMpCInPz09My893sjAyMzA0sBSz9AgvsAAAJ3VK7I"
content-security-policy
script-src 'report-sample' 'nonce-VC4jqRqKT3prRTADB6JRkg' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /_/ContributorLoggingHttp/cspreport;worker-src 'self', script-src 'unsafe-inline' 'unsafe-eval' blob: data: 'self' https://apis.google.com https://ssl.gstatic.com https://www.google.com https://www.googletagmanager.com https://www.gstatic.com https://www.google-analytics.com;report-uri /_/ContributorLoggingHttp/cspreport/allowlist, require-trusted-types-for 'script';report-uri /_/ContributorLoggingHttp/cspreport
cache-control
no-cache, no-store, max-age=0, must-revalidate
cross-origin-opener-policy
same-origin
pragma
no-cache
accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
access-control-allow-credentials
true
permissions-policy
ch-ua-arch=*, ch-ua-bitness=*, ch-ua-full-version=*, ch-ua-full-version-list=*, ch-ua-model=*, ch-ua-wow64=*, ch-ua-form-factors=*, ch-ua-platform=*, ch-ua-platform-version=*
access-control-allow-origin
https://footyroom.co
content-length
0
x-xss-protection
0
server
ESF
GET
H2
200
favicon.ico
footyroom.co/pics/favicons/
15 KB
2 KB
14ms
14ms
Other
image/x-icon
109.201.135.99
NFORCE NForce Ent...
General
Full URL
https://footyroom.co/pics/favicons/favicon.ico
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
109.201.135.99 , Netherlands, ASN43350 (NFORCE NForce Entertainment B.V., NL),
Reverse DNS
Software
nginx /
Resource Hash
0eb78d1031cd4197ec3d3af553c2d99097717002a721a1a439c7ecf3ce2996f5

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000, public
content-encoding
gzip
etag
W/"5d304439-3aee"
pragma
public
expires
Wed, 14 Oct 2026 02:11:14 GMT
date
Mon, 14 Sep 2026 02:11:14 GMT
content-type
image/x-icon
last-modified
Thu, 18 Jul 2019 10:04:41 GMT
server
nginx
vary
Accept-Encoding
POST
H3
204
ping
pagead2.googlesyndication.com/pagead/
0
0
105ms
55ms
Fetch
image/gif
142.251.20.154
Google LLC
General
Full URL
https://pagead2.googlesyndication.com/pagead/ping?e=1
Requested by
Host: securepubads.g.doubleclick.net
URL: https://securepubads.g.doubleclick.net/pagead/managed/js/gpt/m202609040101/pubads_impl.js?cb=122880985
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.20.154 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bx-in-f154.1e100.net
Software
cafe /
Resource Hash
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
0
date
Mon, 14 Sep 2026 02:11:14 GMT
x-xss-protection
0
content-type
image/gif
server
cafe
GET
H2
200
px.gif Show response
ad-delivery.net/
43 B
133 B
22ms
20ms
Fetch
image/gif
2606:4700:10::ac42:948c
Cloudflare
General
Full URL
https://ad-delivery.net/px.gif?ch=2&e=0.921015874498309
Requested by
Host: btloader.com
URL: https://btloader.com/tag?o=6278260873756672&upapi=true
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2606:4700:10::ac42:948c -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
cf4724b2f736ed1a0ae6bc28f1ead963d9cd2c1fd87b6ef32e7799fc1c5c8bda

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
5
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=cpEfJQ==, md5=rUsPYG4PhGW8TEwXCzfhow==
cf-cache-status
HIT
etag
"ad4b0f606e0f8465bc4c4c170b37e1a3"
age
2224
x-goog-stored-content-encoding
identity
expires
Mon, 14 Sep 2026 01:56:21 GMT
x-goog-stored-content-length
43
date
Mon, 14 Sep 2026 02:11:14 GMT
content-type
image/gif
last-modified
Wed, 05 May 2021 19:25:32 GMT
x-guploader-uploadid
AKhXX7Ij0HsF82F-154UYfFX1Gp5cCmGjgS1xTm34ZQjp8FSns2hC9fd1cFeCxd11HNskCSYP4DIRTI
cache-control
public, max-age=86400
x-goog-storage-class
MULTI_REGIONAL
cf-ray
a3abdc1f4af48b7c-AMS
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1620242732037093
content-length
43
server
cloudflare
GET
H3
200
favicon.ico Show response
ad.doubleclick.net/
1 KB
129 B
49ms
48ms
Fetch
image/x-icon
142.251.14.149
Google LLC
General
Full URL
https://ad.doubleclick.net/favicon.ico?ad=300x250&ad_box_=1&adnet=1&showad=1&size=250x250&e=0.44157137192362705
Requested by
Host: btloader.com
URL: https://btloader.com/tag?o=6278260873756672&upapi=true
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.14.149 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f149.1e100.net
Software
sffe /
Resource Hash
d961b08e4321250926de6f79087594975fe20ad1518de8f91eb711af5d1a6ef8
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
report-to
{"group":"ads-doubleclick-media","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/ads-doubleclick-media"}]}
x-content-type-options
nosniff
expires
Tue, 15 Sep 2026 02:11:14 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:14 GMT
content-type
image/x-icon
vary
Accept-Encoding
last-modified
Tue, 08 May 2012 13:08:06 GMT
cache-control
public, max-age=86400
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to="ads-doubleclick-media"
content-length
104
x-xss-protection
0
server
sffe
GET
H2
200
px.gif Show response
ad-delivery.net/
43 B
110 B
20ms
18ms
Fetch
image/gif
2606:4700:10::ac42:948c
Cloudflare
General
Full URL
https://ad-delivery.net/px.gif?ch=1&e=0.38811425680439193
Requested by
Host: btloader.com
URL: https://btloader.com/tag?o=6278260873756672&upapi=true
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2606:4700:10::ac42:948c -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
cf4724b2f736ed1a0ae6bc28f1ead963d9cd2c1fd87b6ef32e7799fc1c5c8bda

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
5
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=cpEfJQ==, md5=rUsPYG4PhGW8TEwXCzfhow==
cf-cache-status
HIT
etag
"ad4b0f606e0f8465bc4c4c170b37e1a3"
age
2224
x-goog-stored-content-encoding
identity
expires
Mon, 14 Sep 2026 01:56:21 GMT
x-goog-stored-content-length
43
date
Mon, 14 Sep 2026 02:11:14 GMT
content-type
image/gif
last-modified
Wed, 05 May 2021 19:25:32 GMT
x-guploader-uploadid
AKhXX7Ij0HsF82F-154UYfFX1Gp5cCmGjgS1xTm34ZQjp8FSns2hC9fd1cFeCxd11HNskCSYP4DIRTI
cache-control
public, max-age=86400
x-goog-storage-class
MULTI_REGIONAL
cf-ray
a3abdc1f4afa8b7c-AMS
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1620242732037093
content-length
43
server
cloudflare
GET
H2
200
dns Show response
ab.dns-finder.com/meta/
2 B
0
0ms
0ms
Fetch
text/plain
34.36.200.111
Google LLC
General
Full URL
https://ab.dns-finder.com/meta/dns
Requested by
Host: btloader.com
URL: https://btloader.com/tag?o=6278260873756672&upapi=true
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.36.200.111 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
111.200.36.34.bc.googleusercontent.com
Software
/
Resource Hash
2689367b205c16ce32ed4200942b8b8b1e262dfc70d9bc9fbc77c49699a4f1df

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
private, max-age=180, stale-if-error=180, stale-while-revalidate=180
access-control-expose-headers
X-Resolver
x-resolver
default
via
1.1 google
access-control-allow-origin
*
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
2
date
Mon, 14 Sep 2026 02:11:13 GMT
content-type
text/plain; charset=utf-8
vary
Origin
GET
H2
200
p.png
silo60.p7cloud.net/ Frame 2244
70 B
534 B
22ms
21ms
Image
image/png
2600:9000:26e8:e000:11:a9de:ec0:93a1
Amazon.com
General
Full URL
https://silo60.p7cloud.net/p.png?visit=prebid&arcid=undefined&ed=setprebid%3A%7B%22v%22%3A617%2C%22tpc%22%3A1%2C%22eng%22%3A0%2C%22sid%22%3A%221k2eqtj090eaa1a6d99e2c4%22%2C%22sd%22%3A%220.00%22%2C%22loc%22%3A%7B%22Country%22%3A%22NL%22%2C%22CountryRegion%22%3A%22NH%22%2C%22City%22%3A%22Amsterdam%22%2C%22PostalCode%22%3A%221096%22%2C%22MetroCode%22%3Anull%2C%22Carrier%22%3Anull%2C%22lat%22%3A%2252.33850%22%2C%22lon%22%3A%224.91680%22%7D%2C%22sess%22%3A%2230hx0fb2ils9uhxs13dcvh%22%2C%22nhtp%22%3A0%2C%22a2%22%3A%5B%5D%2C%22p%22%3A%22https%3A%2F%2Ffootyroom.co%2Fmatches%2F80034717%2Fmanchester-united-vs-sabah-fk%2Freview%22%7D&cb=1789351874548
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2600:9000:26e8:e000:11:a9de:ec0:93a1 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
Software
AmazonS3 /
Resource Hash
44d5041f007d30a9b7079bd3a42ef6da96c4cda10a25b1bcc5a0a6f92b0aadcc

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://silo60.p7cloud.net/if.html?gdpr=false&gdprConsent=false&tpd=true&md=false
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-amz-meta-s3cmd-attrs
atime:1747329020/ctime:1744934005/gid:20/gname:staff/md5:35800716e266902e4fe68ab558d981fb/mode:33188/mtime:1642119937/uid:501/uname:balajirao
etag
"35800716e266902e4fe68ab558d981fb"
age
57943
via
1.1 c6e8f008a950e08db9c0a054276fe95e.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
content-length
70
x-amz-cf-id
75OR-sHhhnxrIF_8GBjEHyUSl7G3H1kr87bEGEDfDau3G-34CXCVVw==
date
Sun, 13 Sep 2026 10:05:31 GMT
content-type
image/png
last-modified
Fri, 16 May 2025 14:07:47 GMT
server
AmazonS3
x-amz-cf-pop
FRA56-P10
x-amz-server-side-encryption
AES256
GET
H2
200
p.png
silo60.p7cloud.net/ Frame 2244
70 B
533 B
24ms
23ms
Image
image/png
2600:9000:26e8:e000:11:a9de:ec0:93a1
Amazon.com
General
Full URL
https://silo60.p7cloud.net/p.png?visit=cohort&arcid=undefined&ed=%7B%22v%22%3A617%2C%22sid%22%3A%221k2eqtj090eaa1a6d99e2c4%22%2C%22grp%22%3A77%2C%22cohorts%22%3A%5B%22AoEGpASS%22%2C%22Pb8F873m%22%2C%22XnfXy2Gc%22%5D%7D&cb=1789351874548
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2600:9000:26e8:e000:11:a9de:ec0:93a1 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
Software
AmazonS3 /
Resource Hash
44d5041f007d30a9b7079bd3a42ef6da96c4cda10a25b1bcc5a0a6f92b0aadcc

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://silo60.p7cloud.net/if.html?gdpr=false&gdprConsent=false&tpd=true&md=false
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-amz-meta-s3cmd-attrs
atime:1747329020/ctime:1744934005/gid:20/gname:staff/md5:35800716e266902e4fe68ab558d981fb/mode:33188/mtime:1642119937/uid:501/uname:balajirao
etag
"35800716e266902e4fe68ab558d981fb"
age
57943
via
1.1 c6e8f008a950e08db9c0a054276fe95e.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
content-length
70
x-amz-cf-id
OOHgvzOhEZ2V2U-uTh8k8UFK1E64SLlZ7Bjf5VN04GcWNasK0bt-qA==
date
Sun, 13 Sep 2026 10:05:31 GMT
content-type
image/png
last-modified
Fri, 16 May 2025 14:07:47 GMT
server
AmazonS3
x-amz-cf-pop
FRA56-P10
x-amz-server-side-encryption
AES256
GET
H2
200
p.png
silo60.p7cloud.net/ Frame 2244
70 B
534 B
23ms
23ms
Image
image/png
2600:9000:26e8:e000:11:a9de:ec0:93a1
Amazon.com
General
Full URL
https://silo60.p7cloud.net/p.png?visit=page&arcid=undefined&ed=%7B%22v%22%3A617%2C%22p%22%3A%22https%3A%2F%2Ffootyroom.co%2Fmatches%2F80034717%2Fmanchester-united-vs-sabah-fk%2Freview%22%2C%22r%22%3A%22%22%2C%22tpc%22%3A1%2C%22sid%22%3A%221k2eqtj090eaa1a6d99e2c4%22%2C%22loc%22%3A%7B%22Country%22%3A%22NL%22%2C%22CountryRegion%22%3A%22NH%22%2C%22City%22%3A%22Amsterdam%22%2C%22PostalCode%22%3A%221096%22%2C%22MetroCode%22%3Anull%2C%22Carrier%22%3Anull%2C%22lat%22%3A%2252.33850%22%2C%22lon%22%3A%224.91680%22%7D%2C%22cbd%22%3A%2220260914%22%2C%22ids%22%3A%22%22%2C%22sess%22%3A%2230hx0fb2ils9uhxs13dcvh%22%2C%22grp%22%3A77%2C%22cohorts%22%3A%5B%22AoEGpASS%22%2C%22Pb8F873m%22%2C%22XnfXy2Gc%22%5D%7D&cb=1789351874548
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2600:9000:26e8:e000:11:a9de:ec0:93a1 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
Software
AmazonS3 /
Resource Hash
44d5041f007d30a9b7079bd3a42ef6da96c4cda10a25b1bcc5a0a6f92b0aadcc

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://silo60.p7cloud.net/if.html?gdpr=false&gdprConsent=false&tpd=true&md=false
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-amz-meta-s3cmd-attrs
atime:1747329020/ctime:1744934005/gid:20/gname:staff/md5:35800716e266902e4fe68ab558d981fb/mode:33188/mtime:1642119937/uid:501/uname:balajirao
etag
"35800716e266902e4fe68ab558d981fb"
age
57943
via
1.1 c6e8f008a950e08db9c0a054276fe95e.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
content-length
70
x-amz-cf-id
Nqu82p1yx4HJgAYYytQX4zz5lbJYtXMdiyIjB_U58k4ycrhgjUBVqA==
date
Sun, 13 Sep 2026 10:05:31 GMT
content-type
image/png
last-modified
Fri, 16 May 2025 14:07:47 GMT
server
AmazonS3
x-amz-cf-pop
FRA56-P10
x-amz-server-side-encryption
AES256
GET
H2
200
px.gif Show response
ad-delivery.net/
43 B
114 B
20ms
20ms
Fetch
image/gif
2606:4700:10::ac42:948c
Cloudflare
General
Full URL
https://ad-delivery.net/px.gif?ch=1&e=0.1491599511035545
Requested by
Host: btloader.com
URL: https://btloader.com/tag?o=6278260873756672&upapi=true
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2606:4700:10::ac42:948c -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
cf4724b2f736ed1a0ae6bc28f1ead963d9cd2c1fd87b6ef32e7799fc1c5c8bda

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
5
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=cpEfJQ==, md5=rUsPYG4PhGW8TEwXCzfhow==
cf-cache-status
HIT
etag
"ad4b0f606e0f8465bc4c4c170b37e1a3"
age
2225
x-goog-stored-content-encoding
identity
expires
Mon, 14 Sep 2026 01:56:21 GMT
x-goog-stored-content-length
43
date
Mon, 14 Sep 2026 02:11:14 GMT
content-type
image/gif
last-modified
Wed, 05 May 2021 19:25:32 GMT
x-guploader-uploadid
AKhXX7Ij0HsF82F-154UYfFX1Gp5cCmGjgS1xTm34ZQjp8FSns2hC9fd1cFeCxd11HNskCSYP4DIRTI
cache-control
public, max-age=86400
x-goog-storage-class
MULTI_REGIONAL
cf-ray
a3abdc20bdc18b7c-AMS
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1620242732037093
content-length
43
server
cloudflare
GET
H2
200
px.gif Show response
ad-delivery.net/
43 B
110 B
19ms
18ms
Fetch
image/gif
2606:4700:10::ac42:948c
Cloudflare
General
Full URL
https://ad-delivery.net/px.gif?ch=2&e=0.8674423912050115
Requested by
Host: btloader.com
URL: https://btloader.com/tag?o=6278260873756672&upapi=true
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2606:4700:10::ac42:948c -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
cf4724b2f736ed1a0ae6bc28f1ead963d9cd2c1fd87b6ef32e7799fc1c5c8bda

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
5
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=cpEfJQ==, md5=rUsPYG4PhGW8TEwXCzfhow==
cf-cache-status
HIT
etag
"ad4b0f606e0f8465bc4c4c170b37e1a3"
age
2225
x-goog-stored-content-encoding
identity
expires
Mon, 14 Sep 2026 01:56:21 GMT
x-goog-stored-content-length
43
date
Mon, 14 Sep 2026 02:11:14 GMT
content-type
image/gif
last-modified
Wed, 05 May 2021 19:25:32 GMT
x-guploader-uploadid
AKhXX7Ij0HsF82F-154UYfFX1Gp5cCmGjgS1xTm34ZQjp8FSns2hC9fd1cFeCxd11HNskCSYP4DIRTI
cache-control
public, max-age=86400
x-goog-storage-class
MULTI_REGIONAL
cf-ray
a3abdc21f9168b7c-AMS
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1620242732037093
content-length
43
server
cloudflare
GET
H3
200
favicon.ico Show response
ad.doubleclick.net/
1 KB
129 B
48ms
48ms
Fetch
image/x-icon
142.251.14.149
Google LLC
General
Full URL
https://ad.doubleclick.net/favicon.ico?ad=300x250&ad_box_=1&adnet=1&showad=1&size=250x250&e=0.10962906051199861
Requested by
Host: btloader.com
URL: https://btloader.com/tag?o=6278260873756672&upapi=true
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.14.149 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f149.1e100.net
Software
sffe /
Resource Hash
d961b08e4321250926de6f79087594975fe20ad1518de8f91eb711af5d1a6ef8
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
report-to
{"group":"ads-doubleclick-media","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/ads-doubleclick-media"}]}
x-content-type-options
nosniff
expires
Tue, 15 Sep 2026 02:11:14 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:14 GMT
content-type
image/x-icon
vary
Accept-Encoding
last-modified
Tue, 08 May 2012 13:08:06 GMT
cache-control
public, max-age=86400
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to="ads-doubleclick-media"
content-length
104
x-xss-protection
0
server
sffe
POST
H3
204
ping
pagead2.googlesyndication.com/pagead/ Frame 9E78
0
0
55ms
55ms
Fetch
image/gif
142.251.20.154
Google LLC
General
Full URL
https://pagead2.googlesyndication.com/pagead/ping?e=1
Requested by
Host: securepubads.g.doubleclick.net
URL: https://securepubads.g.doubleclick.net/pagead/managed/js/gpt/m202609040101/pubads_impl.js?cb=122880985
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.20.154 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bx-in-f154.1e100.net
Software
cafe /
Resource Hash
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
0
date
Mon, 14 Sep 2026 02:11:15 GMT
x-xss-protection
0
content-type
image/gif
server
cafe
POST
H3
204
ping
pagead2.googlesyndication.com/pagead/ Frame 14B4
0
0
56ms
54ms
Fetch
image/gif
142.251.20.154
Google LLC
General
Full URL
https://pagead2.googlesyndication.com/pagead/ping?e=1
Requested by
Host: securepubads.g.doubleclick.net
URL: https://securepubads.g.doubleclick.net/pagead/managed/js/gpt/m202609040101/pubads_impl.js?cb=122880985
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.20.154 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bx-in-f154.1e100.net
Software
cafe /
Resource Hash
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
0
date
Mon, 14 Sep 2026 02:11:15 GMT
x-xss-protection
0
content-type
image/gif
server
cafe
GET
H2
200
usersync
match.adsrvr.org/track/ Frame A4C8
70 B
148 B
31ms
31ms
Image
image/gif
52.223.40.198
Amazon.com
General
Full URL
https://match.adsrvr.org/track/usersync?us_privacy=1---&gdpr=0&gdpr_consent=undefined&ust=image
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
52.223.40.198 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
a6370ebea231e0c9a.awsglobalaccelerator.com
Software
Kestrel /
Resource Hash
8d70b3e6badb6973663b398d297bb32eaedd08826a1af98d0a1cfce5324ffce0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-length
70
date
Mon, 14 Sep 2026 02:11:15 GMT
content-type
image/gif
server
Kestrel
GET
H2
200
px.gif Show response
ad-delivery.net/
43 B
133 B
21ms
21ms
Fetch
image/gif
2606:4700:10::ac42:948c
Cloudflare
General
Full URL
https://ad-delivery.net/px.gif?ch=2&e=0.5603297830966794
Requested by
Host: btloader.com
URL: https://btloader.com/tag?o=6278260873756672&upapi=true
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2606:4700:10::ac42:948c -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
cf4724b2f736ed1a0ae6bc28f1ead963d9cd2c1fd87b6ef32e7799fc1c5c8bda

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
5
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=cpEfJQ==, md5=rUsPYG4PhGW8TEwXCzfhow==
cf-cache-status
HIT
etag
"ad4b0f606e0f8465bc4c4c170b37e1a3"
age
2225
x-goog-stored-content-encoding
identity
expires
Mon, 14 Sep 2026 01:56:21 GMT
x-goog-stored-content-length
43
date
Mon, 14 Sep 2026 02:11:15 GMT
content-type
image/gif
last-modified
Wed, 05 May 2021 19:25:32 GMT
x-guploader-uploadid
AKhXX7Ij0HsF82F-154UYfFX1Gp5cCmGjgS1xTm34ZQjp8FSns2hC9fd1cFeCxd11HNskCSYP4DIRTI
cache-control
public, max-age=86400
x-goog-storage-class
MULTI_REGIONAL
cf-ray
a3abdc249f838b7c-AMS
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1620242732037093
content-length
43
server
cloudflare
POST
H3
200
log_event Show response
www.youtube.com/youtubei/v1/ Frame 6906
28 B
50 B
27ms
23ms
XHR
application/json
142.251.156.119
Google LLC
General
Full URL
https://www.youtube.com/youtubei/v1/log_event?alt=json
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.lHnTAeNCrSc.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywHdVJjs6ktwWXG8Pg3CpN4ZEVjBaQ/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.156.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
scaffolding on HTTPServer2 /
Resource Hash
d7d5e54ad1e33d7ab49c664323ced79cb9723ff15e9764cd0edc3e15208e8336
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
X-YouTube-Client-Name
56
X-YouTube-Ad-Signals
dt=1789351872771&flash=0&frm=2&u_tz=120&u_his=1&u_h=1200&u_w=1600&u_ah=1200&u_aw=1600&u_cd=24&bc=31&bih=-12245933&biw=-12245933&brdim=10%2C10%2C10%2C10%2C1600%2C0%2C1600%2C1200%2C600%2C338&vis=1&wgl=true&ca_type=image
X-Goog-Event-Time
1789351875339
X-YouTube-Client-Version
2.20260911.01.00
Content-Type
application/json
X-YouTube-Page-Label
youtube.embeds.web_20260911_01_RC00
X-YouTube-Page-CL
979642621
X-YouTube-Utc-Offset
120
Referer
https://www.youtube.com/embed/ch_4efPW8xc?rel=0
X-YouTube-Device
cbr=Chrome&cbrver=153.0.0.0&ceng=WebKit&cengver=537.36&cos=X11&cplatform=DESKTOP
X-Goog-Visitor-Id
CgtCR29RR3A5dUhjVSjAr53VBjIoCgJOTBIiEh4SHAsMDg8QERITFBUWFxgZGhscHR4fICEiIyQlJicgYWLfAgrcAjIxLllUPVN3UnN0Z1BEZkl6OG5BaklWWENZNndmN2dTdHFPVmZmUXN3U3U1ZksydnQxVzJxT2E1TlpSYWxiUC1rOEM2bUJPM3RkZEloT3I2dHdZZ09KaDZjS2NyaDVCNWpIeTFEV2NFajV4RkhPcGYyMWtFNlR0YkJzUmx0dFJSVjBKTWNxdUJTd1djQnNqVTB1NFAwSkpCUERxOFVjeXp3TDJUSHVhWTYtdWJLSHloaVRFQzVCaU1iSld6ak9aWGlOblBCbFJJbWF1SGZocktfTExVdmI1UTYtWjJuRGNYVE5ka21NTG82a2FETDNaaVlsS2xnb1FwcU8tM2ZSRG05QkN3QmVVSjItOXVYcEdOOFVROGVNX2NCNG1Qc283Tk5ib0drbUhnZ3hYTGE2eURJYzBpcW5jWUhmY2JTX3RIOUJtZGZmVFlJTTlucVhVeVZwbUx6Zm9NNDA5QQ%3D%3D
X-Goog-Request-Time
1789351875339
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
X-YouTube-Time-Zone
Europe/Amsterdam

Response headers

content-encoding
br
x-content-type-options
nosniff
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
31
date
Mon, 14 Sep 2026 02:11:15 GMT
x-xss-protection
0
content-type
application/json; charset=UTF-8
vary
Origin, X-Origin, Referer
server
scaffolding on HTTPServer2
x-frame-options
SAMEORIGIN
GET
H3
200
favicon.ico Show response
ad.doubleclick.net/
1 KB
129 B
47ms
47ms
Fetch
image/x-icon
142.251.14.149
Google LLC
General
Full URL
https://ad.doubleclick.net/favicon.ico?ad=300x250&ad_box_=1&adnet=1&showad=1&size=250x250&e=0.10194991203856985
Requested by
Host: btloader.com
URL: https://btloader.com/tag?o=6278260873756672&upapi=true
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.14.149 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f149.1e100.net
Software
sffe /
Resource Hash
d961b08e4321250926de6f79087594975fe20ad1518de8f91eb711af5d1a6ef8
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
report-to
{"group":"ads-doubleclick-media","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/ads-doubleclick-media"}]}
x-content-type-options
nosniff
expires
Tue, 15 Sep 2026 02:11:15 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:15 GMT
content-type
image/x-icon
vary
Accept-Encoding
last-modified
Tue, 08 May 2012 13:08:06 GMT
cache-control
public, max-age=86400
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to="ads-doubleclick-media"
content-length
104
x-xss-protection
0
server
sffe
POST
H2
204
csi
csi.gstatic.com/
0
361 B
474ms
163ms
Ping
image/gif
2607:f8b0:4023:2007::5e
Google LLC
General
Full URL
https://csi.gstatic.com/csi?v=2&s=pagead&action=csi_pagead&dmc=32&top=1&puid=1~mu0lwm6f&ctx=0&met.9=1.1ny~2.1zv&met.3=112.2g0_1
Requested by
Host: pagead2.googlesyndication.com
URL: https://pagead2.googlesyndication.com/pagead/js/rum.js?fcd=true
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2607:f8b0:4023:2007::5e Phoenix, United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
scaffolding on HTTPServer2 /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, no-store, must-revalidate
access-control-expose-headers
date,vary,vary,vary,server,content-length
pragma
no-cache
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
access-control-allow-origin
https://footyroom.co
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
0
date
Mon, 14 Sep 2026 02:11:15 GMT
x-xss-protection
0
content-type
image/gif
last-modified
Wed, 21 Jan 2004 19:51:30 GMT
vary
Origin, X-Origin, Referer
server
scaffolding on HTTPServer2
x-frame-options
SAMEORIGIN
GET
H2
200
px.gif Show response
ad-delivery.net/
43 B
114 B
19ms
19ms
Fetch
image/gif
2606:4700:10::ac42:948c
Cloudflare
General
Full URL
https://ad-delivery.net/px.gif?ch=2&e=0.45299259794344815
Requested by
Host: btloader.com
URL: https://btloader.com/tag?o=6278260873756672&upapi=true
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2606:4700:10::ac42:948c -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
cf4724b2f736ed1a0ae6bc28f1ead963d9cd2c1fd87b6ef32e7799fc1c5c8bda

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
5
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=cpEfJQ==, md5=rUsPYG4PhGW8TEwXCzfhow==
cf-cache-status
HIT
etag
"ad4b0f606e0f8465bc4c4c170b37e1a3"
age
2226
x-goog-stored-content-encoding
identity
expires
Mon, 14 Sep 2026 01:56:21 GMT
x-goog-stored-content-length
43
date
Mon, 14 Sep 2026 02:11:15 GMT
content-type
image/gif
last-modified
Wed, 05 May 2021 19:25:32 GMT
x-guploader-uploadid
AKhXX7Ij0HsF82F-154UYfFX1Gp5cCmGjgS1xTm34ZQjp8FSns2hC9fd1cFeCxd11HNskCSYP4DIRTI
cache-control
public, max-age=86400
x-goog-storage-class
MULTI_REGIONAL
cf-ray
a3abdc274d3a8b7c-AMS
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1620242732037093
content-length
43
server
cloudflare
GET
H2
204
i
t.nit.ro/
0
0
130ms
130ms
Fetch
35.244.144.25
Google LLC
General
Full URL
https://t.nit.ro/i?d=ChZOaXRybyBEZXNrdG9wIFZpZGVvIEFkGgVibGFuayipATCsAkJKaHR0cHM6Ly9mb290eXJvb20uY28vbWF0Y2hlcy84MDAzNDcxNy9tYW5jaGVzdGVyLXVuaXRlZC12cy1zYWJhaC1may9yZXZpZXdaJDAxYTA5ZGFlLWNhYmQtNzc1Ny05NGEwLTU0M2IwMDhjMTg3N2ICTkxqAk5IcAOSASA4MDNhZTJkOTA1YmIxODNiYmFlZWIzNDUxODcyMzBiZJoBB2I1NjVjY2WiAQhmbG9hdGluZ7gBANABkRLyAQA%3D
Requested by
Host: s.nitropay.com
URL: https://s.nitropay.com/ads-2321.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
35.244.144.25 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
25.144.244.35.bc.googleusercontent.com
Software
/
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

via
1.1 google
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:15 GMT
vary
Origin
GET
H3
200
favicon.ico Show response
ad.doubleclick.net/
1 KB
129 B
47ms
46ms
Fetch
image/x-icon
142.251.14.149
Google LLC
General
Full URL
https://ad.doubleclick.net/favicon.ico?ad=300x250&ad_box_=1&adnet=1&showad=1&size=250x250&e=0.47181507735218464
Requested by
Host: btloader.com
URL: https://btloader.com/tag?o=6278260873756672&upapi=true
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.14.149 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f149.1e100.net
Software
sffe /
Resource Hash
d961b08e4321250926de6f79087594975fe20ad1518de8f91eb711af5d1a6ef8
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
report-to
{"group":"ads-doubleclick-media","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/ads-doubleclick-media"}]}
x-content-type-options
nosniff
expires
Tue, 15 Sep 2026 02:11:15 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:15 GMT
content-type
image/x-icon
vary
Accept-Encoding
last-modified
Tue, 08 May 2012 13:08:06 GMT
cache-control
public, max-age=86400
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to="ads-doubleclick-media"
content-length
104
x-xss-protection
0
server
sffe
GET
H2
200
px.gif Show response
ad-delivery.net/
43 B
133 B
20ms
20ms
Fetch
image/gif
2606:4700:10::ac42:948c
Cloudflare
General
Full URL
https://ad-delivery.net/px.gif?ch=2&e=0.6233120792070954
Requested by
Host: btloader.com
URL: https://btloader.com/tag?o=6278260873756672&upapi=true
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2606:4700:10::ac42:948c -, , ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
cf4724b2f736ed1a0ae6bc28f1ead963d9cd2c1fd87b6ef32e7799fc1c5c8bda

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
5
access-control-expose-headers
*, Content-Length, Date, Server, Transfer-Encoding, X-GUploader-UploadID, X-Google-Trace
x-goog-hash
crc32c=cpEfJQ==, md5=rUsPYG4PhGW8TEwXCzfhow==
cf-cache-status
HIT
etag
"ad4b0f606e0f8465bc4c4c170b37e1a3"
age
2226
x-goog-stored-content-encoding
identity
expires
Mon, 14 Sep 2026 01:56:21 GMT
x-goog-stored-content-length
43
date
Mon, 14 Sep 2026 02:11:16 GMT
content-type
image/gif
last-modified
Wed, 05 May 2021 19:25:32 GMT
x-guploader-uploadid
AKhXX7Ij0HsF82F-154UYfFX1Gp5cCmGjgS1xTm34ZQjp8FSns2hC9fd1cFeCxd11HNskCSYP4DIRTI
cache-control
public, max-age=86400
x-goog-storage-class
MULTI_REGIONAL
cf-ray
a3abdc29eace8b7c-AMS
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1620242732037093
content-length
43
server
cloudflare
GET
H3
200
favicon.ico Show response
ad.doubleclick.net/
1 KB
129 B
49ms
48ms
Fetch
image/x-icon
142.251.14.149
Google LLC
General
Full URL
https://ad.doubleclick.net/favicon.ico?ad=300x250&ad_box_=1&adnet=1&showad=1&size=250x250&e=0.43132079245948585
Requested by
Host: btloader.com
URL: https://btloader.com/tag?o=6278260873756672&upapi=true
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.14.149 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f149.1e100.net
Software
sffe /
Resource Hash
d961b08e4321250926de6f79087594975fe20ad1518de8f91eb711af5d1a6ef8
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
report-to
{"group":"ads-doubleclick-media","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/ads-doubleclick-media"}]}
x-content-type-options
nosniff
expires
Tue, 15 Sep 2026 02:11:16 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:16 GMT
content-type
image/x-icon
vary
Accept-Encoding
last-modified
Tue, 08 May 2012 13:08:06 GMT
cache-control
public, max-age=86400
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to="ads-doubleclick-media"
content-length
104
x-xss-protection
0
server
sffe
GET
H2
200
sync Show response
srv.scalibur.io/adserver/ Frame 9771
0
186 B
53ms
23ms
Document
application/json
185.167.98.14
CloudWebManage-EU...
General
Full URL
https://srv.scalibur.io/adserver/sync?type=iframe&gdpr=1&gdpr_consent=&us_privacy=1---&gpp=&gpp_sid=
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
185.167.98.14 Amsterdam, Netherlands, ASN41436 (CloudWebManage-EU Kamatera Inc, US),
Reverse DNS
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

Referer
https://footyroom.co/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

access-control-allow-origin
*
age
0
cache-control
no-cache, no-store, must-revalidate
content-length
0
content-type
application/json
date
Mon, 14 Sep 2026 02:11:16 GMT
expires
0
pragma
no-cache
strict-transport-security
max-age=31536000; includeSubDomains
GET
H2
200
sync Show response
srv.scalibur.io/adserver/ Frame 5B97
0
185 B
58ms
16ms
Document
application/json
185.167.98.14
CloudWebManage-EU...
General
Full URL
https://srv.scalibur.io/adserver/sync?type=iframe&gdpr=1&gdpr_consent=&us_privacy=1---&gpp=&gpp_sid=
Requested by
Host: cdn.confiant-integrations.net
URL: https://cdn.confiant-integrations.net/gptprebidnative/202609031720/wrap.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
185.167.98.14 Amsterdam, Netherlands, ASN41436 (CloudWebManage-EU Kamatera Inc, US),
Reverse DNS
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

Referer
https://footyroom.co/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

access-control-allow-origin
*
age
0
cache-control
no-cache, no-store, must-revalidate
content-length
0
content-type
application/json
date
Mon, 14 Sep 2026 02:11:16 GMT
expires
0
pragma
no-cache
strict-transport-security
max-age=31536000; includeSubDomains
GET
H3
204
v
t.nit.ro/
0
0
130ms
130ms
Fetch
35.244.144.25
Google LLC
General
Full URL
https://t.nit.ro/v?d=ChZOaXRybyBEZXNrdG9wIFZpZGVvIEFkGgVibGFuayipATCsAkJKaHR0cHM6Ly9mb290eXJvb20uY28vbWF0Y2hlcy84MDAzNDcxNy9tYW5jaGVzdGVyLXVuaXRlZC12cy1zYWJhaC1may9yZXZpZXdaJDAxYTA5ZGFlLWNhYmQtNzc1Ny05NGEwLTU0M2IwMDhjMTg3N2ICTkxqAk5IcAOSASA4MDNhZTJkOTA1YmIxODNiYmFlZWIzNDUxODcyMzBiZJoBB2I1NjVjY2WiAQhmbG9hdGluZ7gBAMABAcgB6AfQAZES8gEA
Requested by
Host: s.nitropay.com
URL: https://s.nitropay.com/ads-2321.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
35.244.144.25 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
25.144.244.35.bc.googleusercontent.com
Software
/
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

via
1.1 google
alt-svc
h3=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:16 GMT
vary
Origin
GET
H3
204
i
t.nit.ro/
0
0
451ms
450ms
Fetch
35.244.144.25
Google LLC
General
Full URL
https://t.nit.ro/i?d=ChBNYXRjaCBIaWdobGlnaHRzGgVibGFuayhaMMoHQkpodHRwczovL2Zvb3R5cm9vbS5jby9tYXRjaGVzLzgwMDM0NzE3L21hbmNoZXN0ZXItdW5pdGVkLXZzLXNhYmFoLWZrL3Jldmlld1okMDFhMDlkYWUtYzkzOC03ZjJjLThhYmItNWU0YzQ4MzRkM2M4YgJOTGoCTkiSASA4MDNhZTJkOTA1YmIxODNiYmFlZWIzNDUxODcyMzBiZJoBB2I1NjVjY2WiAQdkaXNwbGF5uAEA0AGREvIBAA%3D%3D
Requested by
Host: s.nitropay.com
URL: https://s.nitropay.com/ads-2321.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
35.244.144.25 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
25.144.244.35.bc.googleusercontent.com
Software
/
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

via
1.1 google
alt-svc
h3=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:17 GMT
vary
Origin
GET
H3
204
v
t.nit.ro/
0
0
154ms
154ms
Fetch
35.244.144.25
Google LLC
General
Full URL
https://t.nit.ro/v?d=ChBNYXRjaCBIaWdobGlnaHRzGgVibGFuayhaMMoHQkpodHRwczovL2Zvb3R5cm9vbS5jby9tYXRjaGVzLzgwMDM0NzE3L21hbmNoZXN0ZXItdW5pdGVkLXZzLXNhYmFoLWZrL3Jldmlld1okMDFhMDlkYWUtYzkzOC03ZjJjLThhYmItNWU0YzQ4MzRkM2M4YgJOTGoCTkiSASA4MDNhZTJkOTA1YmIxODNiYmFlZWIzNDUxODcyMzBiZJoBB2I1NjVjY2WiAQdkaXNwbGF5uAEAwAEByAHoB9ABkRLyAQA%3D
Requested by
Host: s.nitropay.com
URL: https://s.nitropay.com/ads-2321.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
35.244.144.25 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
25.144.244.35.bc.googleusercontent.com
Software
/
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

via
1.1 google
alt-svc
h3=":443"; ma=2592000
date
Mon, 14 Sep 2026 02:11:18 GMT
vary
Origin
GET
H2
200
track
srv.scalibur.io/tracker/ Frame 22B1
0
137 B
15ms
15ms
Image
text/plain
185.167.98.14
CloudWebManage-EU...
General
Full URL
https://srv.scalibur.io/tracker/track?pixels=W3sia2V5IjoiMDo1NjpsOmQ6Y2g6Zm9vdHlyb29tLmNvOm5sOjEudGVhZHNiaWRkZXIuZGVmOjk3MHg5MDo6cGkiLCJjb3VudCI6MSwidmFsdWUiOjB9LHsia2V5IjoiMTkwOjU2Omw6ZDpjaDpmb290eXJvb20uY286bmw6MS50ZWFkc2JpZGRlci5kZWY6OTcweDkwOjpiciIsImNvdW50Ijo1LCJ2YWx1ZSI6MH0seyJrZXkiOiIxODY6NTY6bDpkOmNoOmZvb3R5cm9vbS5jbzpubDoxLnRlYWRzYmlkZGVyLmRlZjo5NzB4OTA6OmJyIiwiY291bnQiOjUsInZhbHVlIjowfSx7ImtleSI6IjA6NTY6bDpkOmNoOmZvb3R5cm9vbS5jbzpubDoxLnRlYWRzYmlkZGVyLmRlZjo5NzB4OTA6OnB1IiwiY291bnQiOjEsInZhbHVlIjowfSx7ImtleSI6IjA6NTY6bDpkOmNoOmZvb3R5cm9vbS5jbzpubDoxLnRlYWRzYmlkZGVyLmRlZjo5NzB4OTA6OnZwIiwidmFsdWUiOjUwMDMsImNvdW50IjowfSx7ImtleSI6IjA6NTY6bDpkOmNoOmZvb3R5cm9vbS5jbzpubDoxLnRlYWRzYmlkZGVyLmRlZjo5NzB4OTA6OndwIiwidmFsdWUiOjQ5ODQsImNvdW50IjowfV0%3D
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
185.167.98.14 Amsterdam, Netherlands, ASN41436 (CloudWebManage-EU Kamatera Inc, US),
Reverse DNS
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
access-control-allow-origin
*
content-length
0
date
Mon, 14 Sep 2026 02:11:18 GMT
access-control-allow-methods
GET, POST
GET
H2
200
track
srv.scalibur.io/tracker/ Frame A4C8
0
137 B
14ms
14ms
Image
text/plain
185.167.98.14
CloudWebManage-EU...
General
Full URL
https://srv.scalibur.io/tracker/track?pixels=W3sia2V5IjoiMDo1NjpsOmQ6Y2g6Zm9vdHlyb29tLmNvOm5sOjUuaGVhdnlhZHMubmV3OjMyMHgxODA6OnBpIiwiY291bnQiOjEsInZhbHVlIjowfSx7ImtleSI6IjE5MDo1NjpsOmQ6Y2g6Zm9vdHlyb29tLmNvOm5sOjUuaGVhdnlhZHMubmV3OjMyMHgxODA6OmJyIiwiY291bnQiOjUsInZhbHVlIjowfSx7ImtleSI6IjIwMDo1NjpsOmQ6Y2g6Zm9vdHlyb29tLmNvOm5sOjUuaGVhdnlhZHMubmV3OjMyMHgxODA6OmJyIiwiY291bnQiOjUsInZhbHVlIjowfSx7ImtleSI6IjE4Njo1NjpsOmQ6Y2g6Zm9vdHlyb29tLmNvOm5sOjUuaGVhdnlhZHMubmV3OjMyMHgxODA6OmJyIiwiY291bnQiOjUsInZhbHVlIjowfSx7ImtleSI6IjA6NTY6bDpkOmNoOmZvb3R5cm9vbS5jbzpubDo1LmhlYXZ5YWRzLm5ldzozMjB4MTgwOjpwdSIsImNvdW50IjoxLCJ2YWx1ZSI6MH0seyJrZXkiOiIwOjU2Omw6ZDpjaDpmb290eXJvb20uY286bmw6NS5oZWF2eWFkcy5uZXc6MzIweDE4MDo6dnAiLCJ2YWx1ZSI6NTAwMSwiY291bnQiOjB9LHsia2V5IjoiMDo1NjpsOmQ6Y2g6Zm9vdHlyb29tLmNvOm5sOjUuaGVhdnlhZHMubmV3OjMyMHgxODA6OndwIiwidmFsdWUiOjQ5ODcsImNvdW50IjowfV0%3D
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
185.167.98.14 Amsterdam, Netherlands, ASN41436 (CloudWebManage-EU Kamatera Inc, US),
Reverse DNS
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://footyroom.co/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
access-control-allow-origin
*
content-length
0
date
Mon, 14 Sep 2026 02:11:18 GMT
access-control-allow-methods
GET, POST

Failed requests

These URLs were requested, but there was no response received. You will also see them in the list above.

Domain
ib.adnxs.com
URL
https://ib.adnxs.com/getuidp?callback=aspan.setXandr
Domain
ssb-global.smartadserver.com
URL
https://ssb-global.smartadserver.com/api/bid?callerId=169

Verdicts & Comments Add Verdict or Comment

270 JavaScript Window variables Go Pro

Only in urlscan Pro

Inspect and pivot on JavaScript variables, identifiers, and other key site metadata data with urlscan Pro. Reveal and search on client-side frameworks, runtime variables, and custom values.
Click for more information
Free trials of urlscan Pro are available.

These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.

object| 0 object| 1 object| 2 object| 3 object| 4 object| 5 object| 6 object| 7 object| 8 object| 9 object| 10 object| 11 object| 12 object| 13 object| nitroAds object| dataLayer function| showGiftPopup function| showGiftPopupMobile object| ads object| nads object| nitro object| napbjs object| _pbjsGlobals object| mnet object| __tcfapi_queue function| __tcfapi object| scalibur object| googletag object| WebFont string| SITEURL object| DataStore boolean| isPrerenderRequest function| $ function| jQuery object| angular object| webpackJsonp object| regeneratorRuntime function| _ function| io function| ABNS string| ABNSh object| ABNSl string| GoogleAnalyticsObject function| ga boolean| __nitroFloatingVideoInited object| NREUM object| jQuery1102015754628622230193 object| default_ContributorServingResponseClientJs object| _F_toggles_default_ContributorServingResponseClientJs object| __googlefc string| __fcInvoked string| __fcexpdef object| ggeac string| NmMxYzZmYjY4MzQ5ZmM3ZGxvYWRlcl9qcw== string| NmMxYzZmYjY4MzQ5ZmM3ZGNhY2hlZF9qcw== object| googlefc object| __fcInternalApiManager boolean| __fcInternalApiPostMessageReady function| __uspapi object| __uspapiManager boolean| __uspapiPostMessageReady object| __gppEventListeners function| __gpp object| __gppManager boolean| __gppPostMessageReady object| _CLOB object| clicky object| clicky_custom object| clicky_site_ids object| _cgen object| _cgen_custom object| __scaliburPatches function| CC object| CleverCore function| ABN object| pr number| pos string| k number| v object| e object| b object| nitroAdsCustomConsents string| nitroAdsPublisherCC object| apstag function| clearImmediate function| setImmediate object| atsenvelopemodule object| ats object| google_tag_data object| google_js_reporting_queue object| gaplugins object| gaGlobal object| gaData object| google_tag_manager object| wf object| __bt_edge_data object| __bt object| __bt_intrnl boolean| __bt_already_invoked object| __bt_tag_d number| __aps_slice object| _aps boolean| apstagLOADED object| apscustom object| google_reactive_ads_global_state function| onYouTubeIframeAPIReady object| pbjs function| _arcspan_page_inputs_from_record function| _arcspan_page_from_arcobj1 function| _arcspan_arcobj1_from_page function| _arcspan_as_list function| _arcspan_token_text function| _arcspan_keyword_pieces function| _composite_eval_setup function| _composite_has_scoh function| _composite_page_from_arcobj1 function| _composite_inputs_from_page function| _composite_log_error function| _composite_apply_results function| evaluate_composite_cohorts function| _yieldToBrowser function| evaluate_composite_cohorts_chunked object| _a1cfg object| aspan object| arcobj1 function| aspan_extern object| arcobj2 object| _aj1 function| aspan_extern_pre function| _bmb function| ha object| lotame_sync_16576 object| __id5_finalization_registry object| ID5 object| id5_pbjs_et boolean| 9092fbce-4866-49f8-9990-f5444f8c4c01 number| google_global_correlator function| lotameIsCompatible function| sync16576_aa function| sync16576_c function| sync16576_ca object| sync16576_g function| sync16576_h function| sync16576_ea function| sync16576_ha object| sync16576_ object| sync16576_na object| sync16576_oa object| sync16576_p object| sync16576_y object| sync16576_Ba function| sync16576_a function| sync16576_b function| sync16576_f function| sync16576_da function| sync16576_fa function| sync16576_i function| sync16576_ga function| sync16576_j function| sync16576_k function| sync16576_l function| sync16576_ia function| sync16576_m function| sync16576_n function| sync16576_o function| sync16576_ka function| sync16576_ja function| sync16576_la function| sync16576_ma function| sync16576_q function| sync16576_s function| sync16576_t function| sync16576_u function| sync16576_pa function| sync16576_qa function| sync16576_v function| sync16576_ra function| sync16576_w function| sync16576_x function| sync16576_r function| sync16576_z function| sync16576_sa function| sync16576_ta function| sync16576_ua function| sync16576_A function| sync16576_B function| sync16576_C function| sync16576_va function| sync16576_D function| sync16576_E function| sync16576_F function| sync16576_H function| sync16576_J function| sync16576_I function| sync16576_K function| sync16576_L function| sync16576_G function| sync16576_wa function| sync16576_xa function| sync16576_ya function| sync16576_za function| sync16576_Aa function| sync16576_M function| sync16576_N function| sync16576_Ca function| sync16576_O function| sync16576_Da function| sync16576_Ea function| sync16576_Fa function| sync16576_P function| sync16576_Ga function| sync16576_Ha function| sync16576_Ia function| sync16576_Ja function| sync16576_Q function| sync16576_Ka function| sync16576_R function| sync16576_S function| sync16576_T function| sync16576_U function| sync16576_La function| sync16576_V function| sync16576_W function| sync16576_X function| sync16576_Y function| sync16576_Z function| sync16576__ function| sync16576_0 function| sync16576_Ma function| sync16576_1 function| sync16576_Oa function| sync16576_Na function| sync16576_2 function| sync16576_Qa function| sync16576_Ra function| sync16576_Pa function| sync16576_Sa function| sync16576_Va function| sync16576_Ua function| sync16576_Ta function| sync16576_Xa function| sync16576_Za function| sync16576_Wa function| sync16576_5 function| sync16576_Ya function| sync16576_1a function| sync16576_2a function| sync16576_0a function| sync16576__a function| sync16576_6 function| sync16576_3 function| sync16576_4 function| sync16576_7 function| sync16576_8 function| sync16576_3a function| sync16576_4a function| sync16576_5a function| sync16576_6a function| sync16576_9 function| sync16576_7a function| sync16576_$ function| sync16576_8a function| sync16576_9a function| sync16576_$a object| auvars number| google_srt object| _google_rum_ns_ object| PublisherCommonId object| closure_lm_433310 object| closure_lm_72563

34 Cookies Go Pro

Only in urlscan Pro

Review, search, and pivot on browser cookies and persistence site data to see how a site tracks users and keeps sessions alive across visits.
Click for more information
Free trials of urlscan Pro are available.

Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.

Domain/Path Expires Name / Value
footyroom.co/matches/80034717/manchester-united-vs-sabah-fk 1969-12-31
23:59:59
Name: geoip
Value: SE
footyroom.co/advertise 1969-12-31
23:59:59
Name: geoip
Value: SE
.footyroom.co/ 1970-01-21
17:03:58
Name: user_country
Value: The+Netherlands
.footyroom.co/ 1970-01-21
17:03:58
Name: user_country_code
Value: NL
footyroom.co/ 1970-01-22
02:38:31
Name: tracker
Value: a367408866633c829de44316a883337b
footyroom.co/ 1970-01-21
17:45:43
Name: XSRF-TOKEN
Value: steX81dkvMB8jVtXW2TWQXEFpR5vwASOD5SxaqdY
footyroom.co/ 1970-01-21
17:02:39
Name: fr_session
Value: AY8nVOQEySMR9JQRnMHWocAqccQYDLJ8MPLTfFz8
.nitropay.com/ 1970-01-21
17:02:33
Name: __cf_bm
Value: 7bkuybUjIq_z5Pmvp5KVlnq05tz3sbS7chUfdk2CEtE-1789351872.0750837-1.0.1.1-grIOqR1TGFxlnSC2bclQZXTOc9UXoxSzBZx_CbBlxkVRXWesbgCjWiTv93km1eXBm7UIbLnzkSt8CjEu7Bi.e2tUd68d_cw742FQlv4dZL78gncODdXHsFNhr3usZDFi
footyroom.co/ 1969-12-31
23:59:59
Name: io
Value: 2RYDuym3aogoqiIXAlnK
.cleverwebserver.com/ 1970-01-21
17:02:33
Name: __cf_bm
Value: Pv4IT4lwTYzSMa4sD.hov7T08gNmy7CuMWeBTqORwJg-1789351872.3814712-1.0.1.1-rcNKVF_MwCSH5OrugRVcOZ.hTmyY3_2glZc6vhMFRF0YZKQazdU1lA2FhK3GnP9hrAjoi_i2wEw9GAF6J9aYxHMwBpDGGxaNYgHd_7V2xkfBDGUT5f8hoa.nv194uLht
.youtube.com/ 1970-01-21
21:21:43
Name: __Secure-YNID
Value: 21.YT=SwRstgPDfIz8nAjIVXCY6wf7gStqOVffQswSu5fK2vt1W2qOa5NZRalbP-k8C6mBO3tddIhOr6twYgOJh6cKcrh5B5jHy1DWcEj5xFHOpf21kE6TtbBsRlttRRV0JMcquBSwWcBsjU0u4P0JJBPDq8UcyzwL2THuaY6-ubKHyhiTEC5BiMbJWzjOZXiNnPBlRImauHfhrK_LLUvb5Q6-Z2nDcXTNdkmMLo6kaDL3ZiYlKlgoQpqO-3fRDm9BCwBeUJ2-9uXpGN8UQ8eM_cB4mPso7NNboGkmHggxXLa6yDIc0iqncYHfcbS_tH9BmdffTYIM9nqXUyVpmLzfoM409A
.youtube.com/ 1969-12-31
23:59:59
Name: YSC
Value: 1HLx7_CFDnM
.youtube.com/ 1970-01-21
21:21:43
Name: __Secure-ROLLOUT_TOKEN
Value: CMCu4KTk9arNUhD_4_CV_-yWAxj_4_CV_-yWAw%3D%3D
.youtube.com/ 1970-01-21
21:21:43
Name: VISITOR_INFO1_LIVE
Value: BGoQGp9uHcU
.youtube.com/ 1970-01-21
21:21:43
Name: VISITOR_PRIVACY_METADATA
Value: CgJOTBIiEh4SHAsMDg8QERITFBUWFxgZGhscHR4fICEiIyQlJicgYQ%3D%3D
.footyroom.co/ 1970-01-22
01:48:07
Name: _nitroID
Value: 803ae2d905bb183bbaeeb345187230bd
.traffmovie.com/ 1970-01-22
01:48:07
Name: AU
Value: 44ea104165644f82
.footyroom.co/ 1970-01-22
02:38:31
Name: _ga
Value: GA1.2.1302944229.1789351873
.footyroom.co/ 1970-01-21
17:03:58
Name: _gid
Value: GA1.2.112525078.1789351873
.footyroom.co/ 1970-01-21
17:02:31
Name: _gat
Value: 1
silo60.p7cloud.net/ 1970-01-21
17:02:32
Name: _t
Value: 777
.p7cloud.net/ 1970-01-21
17:02:32
Name: arcid_60
Value: silo60:ae025c43-b265-4e9c-856f-17be8af12f8f
.tapad.com/ 1970-01-21
18:28:55
Name: TapAd_TS
Value: 1789351873718
.tapad.com/ 1970-01-21
18:28:55
Name: TapAd_DID
Value: 41f39c51-bdee-4c46-92c7-33435d9ad432
.tapad.com/ 1970-01-21
18:28:55
Name: TapAd_3WAY_SYNCS
Value:
.footyroom.co/ 1970-01-22
02:38:31
Name: _ga_CGXL08N85B
Value: GS2.2.s1789351873$o1$g0$t1789351873$j60$l0$h240706014
footyroom.co/ 1970-01-21
18:28:55
Name: pbjs-unifiedid
Value: %7B%22TDID_LOOKUP%22%3A%22FALSE%22%2C%22TDID_CREATED_AT%22%3A%222026-09-14T02%3A11%3A13%22%7D
footyroom.co/ 1970-01-21
18:28:55
Name: pbjs-unifiedid_cst
Value: VyxHLMwsHQ%3D%3D
footyroom.co/ 1970-01-21
18:28:55
Name: pbjs-unifiedid_last
Value: Mon%2C%2014%20Sep%202026%2002%3A11%3A13%20GMT
.id5-sync.com/ 1970-01-21
19:12:07
Name: id5
Value: 9338d38e-81ee-733a-bc25-ff39f65475dc#1789351873892#1
.footyroom.co/ 1970-01-22
02:24:07
Name: FCCDCF
Value: %5Bnull%2Cnull%2Cnull%2Cnull%2Cnull%2Cnull%2C%5B%5B32%2C%22%5B%5C%22eddfd766-2ab3-4b39-bdae-582c30ef5ce7%5C%22%2C%5B1789351872%2C684000000%5D%5D%22%5D%5D%5D
prebid.media.net/ 1970-01-21
21:21:43
Name: receive-cookie-deprecation
Value: 1
.footyroom.co/ 1970-01-22
01:48:07
Name: FCNEC
Value: %5B%5B%22AKsRol-nnvShhGw2VL0_YBy34zcDut_Y97j4VntqTXRWidKz0U44frG9a5hoTNo--W4qgtcr44mkQ7a9xc_jEI7_rJOD57d285Ot3ms0y6P6YHEIJQtKTJXJE12waEJf95ZboCkuScqonOOyKpuc593be7zfeb2HmA%3D%3D%22%5D%5D
footyroom.co/ 1970-01-21
17:02:33
Name: aspan_s
Value: 30hx0fb2ils9uhxs13dcvh

9 Console Messages

A page may trigger messages to the console to be logged. These are often error messages about being unable to load a resource or execute a piece of JavaScript. Sometimes they also provide insight into the technology behind a website.

Source Level URL
Text
rendering warning URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review(Line 298)
Message:
[]Automatic fallback to software WebGL has been deprecated. Please use the --enable-unsafe-swiftshader flag to opt in to lower security guarantees for trusted content.
rendering warning URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review(Line 298)
Message:
[]Automatic fallback to software WebGL has been deprecated. Please use the --enable-unsafe-swiftshader flag to opt in to lower security guarantees for trusted content.
other warning URL: https://ajax.googleapis.com/ajax/libs/jquery/1.10.2/jquery.min.js(Line 4)
Message:
Unrecognized feature: 'web-share'.
recommendation verbose URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Message:
[DOM] Input elements should have autocomplete attributes (suggested: "current-password"): (More info: https://goo.gl/9p2vKq) %o
rendering warning URL: https://footyroom.co/matches/80034717/manchester-united-vs-sabah-fk/review
Message:
[]Automatic fallback to software WebGL has been deprecated. Please use the --enable-unsafe-swiftshader flag to opt in to lower security guarantees for trusted content.
rendering warning URL: https://www.youtube.com/embed/ch_4efPW8xc?rel=0
Message:
[]Automatic fallback to software WebGL has been deprecated. Please use the --enable-unsafe-swiftshader flag to opt in to lower security guarantees for trusted content.
network error URL: https://cdn.api.btloader.com/device?orgid=6278260873756672&fullVersionList=%5B%7B%22brand%22%3A%22Chromium%22%2C%22version%22%3A%22153.0.0.0%22%7D%2C%7B%22brand%22%3A%22Google+Chrome%22%2C%22version%22%3A%22153.0.0.0%22%7D%2C%7B%22brand%22%3A%22Not_A+Brand%22%2C%22version%22%3A%228.0.0.0%22%7D%5D&upapi=true
Message:
Failed to load resource: the server responded with a status of 403 ()
rendering warning URL: https://www.youtube.com/embed/ch_4efPW8xc?rel=0
Message:
No available adapters.
network error URL: https://idsync.rlcdn.com/713229.gif?partner_uid=silo60:ae025c43-b265-4e9c-856f-17be8af12f8f
Message:
Failed to load resource: the server responded with a status of 451 ()

Security Headers

This page lists any security headers set by the main page. If you want to understand what these mean and how to use them, head on over to this page

Header Value
Strict-Transport-Security max-age=2592000; includeSubDomains
X-Frame-Options sameorigin

Indicators

This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.

a.ad.gt
ab.dns-finder.com
ad-delivery.net
ad.doubleclick.net
ajax.googleapis.com
analytics.google.com
ats-wrapper.privacymanager.io
btloader.com
btlr.sharethrough.com
c.amazon-adsystem.com
call.cleverwebserver.com
cdn.api.btloader.com
cdn.btloader.com
cdn.confiant-integrations.net
cdn.footyroom.co
cdn.hadronid.net
cdn.id5-sync.com
cdn.jsdelivr.net
cdn.traffmovie.com
cdnjs.cloudflare.com
code.angularjs.org
config.aps.amazon-adsystem.com
csi.gstatic.com
d3j8vl19c1131u.cloudfront.net
direct.adsrvr.org
fastlane.rubiconproject.com
floors.nitropay.com
fonts.googleapis.com
fonts.gstatic.com
footyroom.co
fundingchoicesmessages.google.com
geo.privacymanager.io
googleads.g.doubleclick.net
hb.minutemedia-prebid.com
i.ytimg.com
ib.adnxs.com
id.hadron.ad.gt
id5-sync.com
idsync.rlcdn.com
image6.pubmatic.com
images.footyroom.com
imasdk.googleapis.com
in.getclicky.com
jnn-pa.googleapis.com
lal.p7cloud.net
lb.eu-1-id5-sync.com
location.p7cloud.net
match.adsrvr.org
pagead2.googlesyndication.com
pixel.rubiconproject.com
pixel.tapad.com
prebid.media.net
rumcdn.geoedge.be
s.nitropay.com
s0.2mdn.net
scripts.cleverwebserver.com
secure.cdn.fastclick.net
securepubads.g.doubleclick.net
silo60.p7cloud.net
srv.scalibur.io
ssb-global.smartadserver.com
static.doubleclick.net
static.getclicky.com
stats.g.doubleclick.net
t.nit.ro
tags.crwdcntrl.net
targeting.unrulymedia.com
ua.p7cloud.net
ui.cleverwebserver.com
us-u.openx.net
vi.ml314.com
www.google-analytics.com
www.google.com
www.googletagmanager.com
www.gstatic.com
www.youtube.com
yt3.ggpht.com
z.cdn.traffmovie.com
ib.adnxs.com
ssb-global.smartadserver.com
103.231.98.107
104.16.225.240
104.17.25.14
104.18.3.78
109.201.135.99
13.226.244.59
13.33.187.36
135.125.170.108
135.125.170.28
142.250.154.94
142.251.110.100
142.251.127.156
142.251.13.154
142.251.14.149
142.251.150.4
142.251.156.119
142.251.20.154
143.204.173.87
143.204.181.10
151.101.1.195
172.64.144.166
178.162.196.143
18.245.31.123
185.167.98.14
2.16.241.214
2001:4860:4802:36::181
2001:4860:4826:400::
2001:4860:4845:400::
2600:9000:2013:ac00:4:b37b:9440:93a1
2600:9000:208a:a00:18:f839:ac80:21
2600:9000:20e8:fa00:3:c079:7fc0:93a1
2600:9000:2251:f600:15:c08e:ec40:93a1
2600:9000:26e8:a200:11:a9de:ec0:93a1
2600:9000:26e8:e000:11:a9de:ec0:93a1
2600:9000:28eb:cc00:12:a1d3:a3c0:93a1
2602:803:c003:200::21
2606:4700:10::6814:14bd
2606:4700:10::6814:2396
2606:4700:10::ac42:948c
2606:4700:10::ac42:a677
2606:4700:10::ac42:a937
2606:4700:10::ac42:ab85
2606:4700:4405::6812:21f7
2607:f8b0:4023:2007::5e
2a00:1450:4001:c0f::5f
2a00:1450:4001:c13::84
2a00:1450:4001:c13::8a
2a00:1450:4001:c15::5f
2a00:1450:4001:c15::61
2a00:1450:4001:c15::66
2a00:1450:4001:c15::77
2a00:1450:4001:c17::5e
2a00:1450:4001:c17::77
2a00:1450:4001:c21::94
2a00:1450:4001:c21::9a
2a00:1450:4001:c25::95
2a04:4e42:400::485
34.111.113.62
34.36.200.111
34.36.209.34
34.98.64.218
35.201.104.135
35.207.108.208
35.244.144.25
35.244.174.68
46.228.165.115
52.223.40.198
52.223.6.21
63.180.245.66
69.173.144.165
95.211.37.134
007d02e9c6729b59d21f2400bf2e4bd98a637be339b583ca58f418013909fe54
00f3330eef64aed5914fcd3154c47b91076257797ed9831cac13aa9e239df47a
01ba4719c80b6fe911b091a7c05124b64eeece964e09c058ef8f9805daca546b
0208b97373fa96b5919799803d8baeff65f5ac1e59b51efb7662ac66362f4c08
024a9fdfcbe8e3062bde5451967c598720afa912cfc409196973d5cd5afb3165
0579619786f40ef19b66506851c5d4a0e65b1d04212419bb8f9b14adac695f0c
06703c2a3084400650b4ee792386b425153efa8189a3c8de4458adc7c6446a74
06b99248a163333e36980a6cfb756f1a7de60fa49517162b87b1a44d5d48f844
0b7fb7d01e2b5aeddb1e38dc1ecc55635ba5c59efa8aba067925b6980ff91d1c
0eb78d1031cd4197ec3d3af553c2d99097717002a721a1a439c7ecf3ce2996f5
15b0bf6a136be84146f328db0a1d9af813441d63f2910f1296a7eebbabd10033
178baf0ac7985ada858fb5fcbb47e669b25fbbc752f929fa1e9d640e4cfa1de5
179110bbab4e2b0a8a5407d05e02c57cc1d98fcc745c3633e4ea763b0eda664b
18120a6bee05cd823d5f4ab0c52006863a059a5d6c535c790a31bdd2ee8c45e7
1b7e701706f765d9c424566f23012446200c4731de24d1616d656d61ed252055
1c15b7b8a29622472026b9de49587091037c06d04f00bca8c5cf98bfd4fc7c7e
1cb3f65a88a78e2ec2bbf0aca1a9a084cbc2ad976ca4aa77f5f55a16ba6e55ad
1d3981e2a7a649628869697e8060bd05d9385b20be2330fc436f4bbab1534694
1d9ef22e5168f1b0cdafc63048b210705b4edd54378c874fdc58843110de375e
1e6a48f545fe9a849b2e085519ede5fdf1893b4b273b73f3ba7ce0df22397277
1e6f131e5c23998532caa01dec741cd746efdb7364cffaf33a43f227aaa0d458
1ebb685e3aec008b3c941ea272149fa403a676e89235c76dc2c1f9e62db1430f
1f925ed18b954f626b23e794fee28b231aea291baf15dcd412c1e13331335581
1fa4bc01369d2d854e9fc64a454320682173fc228d05c0d5c5e088d15bdc3af1
20b535fa80c8189e3b87d1803038389960203a886d502bc2ef1857affc2f38d2
21708fe6f20640f454dc6792440b20ebd67fba3a60b36c2a7267e30b651e9df0
221f201b878a88ffb7c038ce5b70ecf20fcb5595557c7ec95f3f491ba42e59f0
22c197c6555b3b8e701fce02390a145bc268f3d74a4e652c549fd1557f7bac53
2689367b205c16ce32ed4200942b8b8b1e262dfc70d9bc9fbc77c49699a4f1df
3656ad0b9309abc5993e3cd41a5b83b18ae7e261fd007d16cb44d5e102520632
36b4cda222f74c9ceaebf5b2dfca34066f00f0eb139c4904247de0aa869a0d69
37ec5817a0032426b8e9dd7991df9bc48d38d0b4ad358a8890dbe02fb92be13c
380da8311b69d9d978d9219e8547a526d75d873d5e0ac5a2bbdc5bb0da01f960
39d17ad943268e4ac1ae837a9e8392803159ea9115dc5f9992fe4589e9787877
3a16b6fe0a26fecd8d0bfb084c415b3981f3ba2046ac0983d1c3b1b2859be26c
3eb10792d1f0c7e07e7248273540f1952d9a5a2996f4b5df70ab026cd9f05517
41bde1003b9ce5cb663e859474f0c982ce1985c6012710343704e05c1b7072e8
4411aa744346b0a2f2b92b31a84c714a40ee384e60345816a03c253e0cb7db5f
44136fa355b3678a1146ad16f7e8649e94fb4fc21fe77e8310c060f61caaff8a
44d5041f007d30a9b7079bd3a42ef6da96c4cda10a25b1bcc5a0a6f92b0aadcc
45bc6978e281a938d9485dcbf0859159b24e2f7c9b8b0fafc120b9606e0ea8b1
46d313ada07980694b111d0590a05c6970a6642402c64292fdd5e6ecc484a046
46d6a0984aa795b764141232671160e61bdcc49e900de67ca6b35bae25b1ebdd
46f2212adc3d46f1cf1c201e95361d29258a5bc2f0f6d1c550d4482d2030b04d
47ad943b070f25adcb4e1a50ebf5fc0da79a2222ffcefb9d77820cb805a77f71
4b5587d97b275236a91526ee6ae980e45474af35956f86c242f30ccb4d618ce2
4ca933d11ea854b96a4e68074962248402e5ac3e71b1ff4b8aac7c81485f8ebb
4cde20607a069eefd4289f5f75cbacac271db09ca6fb9fbfaf615876ee6f9257
4f5a68894720ca8cfd19bb5ab499e5c83fa7de051a4bb037494e589999be8247
52627dfef9258889938f55063996e3ff713dd22756730d5ef4418622587f1b3a
5299891a420281a888e79002f45eccaf4d9a78203d3eb47a5cce24122f38ff79
555e95e5af65cfd867790ac83d0f93780e6a63078135648b21c4fb935c1e04b0
563e1f9a52535fbc9800a8a1047cb55e4a913a751da2c6a1ee9b4e9ed9ef4302
5d055cefe58e49c6c6c4b14972a9c9746edba9ebbe4dc3f02d1ddd96a7555a7a
60542d1c58f93ceb6dd83b360875978f07a0297d78989eef816778137f8c0159
61407ce1df311cd5bcff27d026e281a184a2cffe8fa24c3a2758ed2f2624b317
61423dca26858bc9c29ff972df1cf3207de529f3c8892577fb01713d200d2b42
622c4f1f3296bfb04db7db0948903796d7794a19ddb8ade6aed50c309fe1fcb6
6333d5adf5474f221fea5509b5c056acf0b11f959961cbb3d6a95fddcd9640e0
63fc76ea52a47bd52265c2e4cccc527ce2eac7576c34cd942c4a9ef310fc9009
65c58dc713ec4def44139bd459f870adbf29a0a86bf74775a2ed33658441274f
65fdf886bd4624b31647215def1ee1bb13c56557f180e8689f4070f23247b08d
66f1c1ed9421630251a28dc56a48a17da8acecd8eefa41aaf44baab0fd7d8c7a
691491f1fc8badab623e1be56f92cc2d98c462b16617c67e1e288d6b061444bc
691cd1d9b4c0cdf31a1dcf04259c86f92c85e69f6622abab7964d81e36890691
6a5d3217bae4baa9358b0bddfc3b305154aa34fecb52735e3652c3096f3eb899
6ba2ebdb157f9d5409d63533d17a93dd308e702bcb9884573a0a169d8717bf1e
6bab55ba848dbc6da9af1a8b805f4c9d551b503f0c3f077a04dffba5b03d6372
6c0a003ae339daa9b04d224ffe58f4d0493097502cfb0428f90f33b3a2a3f144
6d51cc4c1338720545dc666f4df3fe1a78b2e9d97058dad6afe5c9353b60312c
6d91bc6120d9947b8c5624f5e87fed0eb850c9140a2fe1c1bfc9987851431e79
6edb5275ff2227bece0bf3341bdabb6f2f6d8ff1fb31d726d263eb317996f4b3
6fa88a20839537ae66da730e5bd183035265176d972bc8df075b89da0c6186ea
7948dd3e7b6e12634b2eaa474d1caa8d6f86e54a095fd273838a8c2f335708ec
7cdf854b7f64ff5d0d42e9aee3b262acfb6c3b319e9f728b471d37d47015ab9a
7de3c31102bcdca0518cfe683d5ebde8774aa00b726578d55ab513c13bbc5b07
7f11fe296be962098dd3f887faf2a349c44b45761732dd016936f31f3cfdcace
81016ac6be850b72df5d4faa0c3cec8e2c1b0ba0045712144a6766adfad40bee
825929ab83c989bfbfcbcfa47d0bab1eeea39bb18436294ed531fbd252038abc
83ecca4db46f0b53049489868d70337081985ba5557d42bd397609e7d59bfcc9
846949c5a40e3ffbb702473e54dfac0646541aa624a844369b6e24e51ddaf96b
86b742cfa596799c1a5856ba629afdd7b7b1e5478112bbb2101d126b9a2c75d9
899930caa73eef59d0670826b7dd81ad480a8bb66c6074ff6c79f23928d0e6c6
89a15e9c40bc6b14809f236ee8cd3ed1ea42393c1f6ca55c7855cd779b3f922e
8c15e64745dad33d026db42c28b620ee9f4f16d7dbffb3f24649fc69bb64205a
8d70b3e6badb6973663b398d297bb32eaedd08826a1af98d0a1cfce5324ffce0
91dc55df3cb71d55183ce0f0cacef7f3455f34673d1a433baf045251448c0e66
94c23c75d87c8af7ad4ab772d42c45f78c44bd9c99b89b0d512296aef53bb757
94d264bd436b015615096ddd81b9ea69a29930139d2a4231232c27a936704ca5
97dd4dda84363c123e3a555000381aebdc578c855bd496e761674011f3654766
99b8168901ae10ac07f3a2dfb99688ce9ccebad0c01b3f245f995d075d6075e1
9a6f174d593d8404d55c3ba5b8ddc199d63196b87c1cf40b061fe0266660af3d
9cbe7017ccc2b87de6f0754ca4b028c9052243ee4419ff648f4585f1787b4f67
9d7e2af808c9eb886aa9a96d4914114a87842afae4fd68a732dae72969fe189d
9dffbd45ce48bf5e8eeb90b3d8567f8270f217c174de81fe3693d6dcdbaa1588
a05868fe2ac912e68abd58799623f01aa68e8bd4d0afc86c73b17c4528073bb8
a31ae035f391740bef8c134ff847e1e5de9bd8fe998ede383df0e5374f007474
a5cc31c26956638a4a4039d99aa5ca121d1325d9938c3449bca213f9a7fc3b8f
aa03dc59bdca72631d2301e4297cfa030bd31b907dc138e7b973d12311c90a22
aa798163f47e11eda70c68669b4e75f7f694f429fceba154b606263a583b57b3
abf75184a8bf40f8ab07d4bb68ab98f778a59e93591cd7e0627b465238e2f6b4
adacc49bf84c6e75cfe776430e55282e25b96c51bd4a0f338264322f8b8fcbd3
b2d9eab8aa663fec87b5869aa1e13e45c2bd8e125b4dcfdc10b07f7f6179791d
b69ef083bc12058a1b5cf6e59d261c3914e079869a3c126ac134ec4e119509f5
b92d631998d0b44cc058cdc300030cc9dc0b19d0ba45dde0f0eba3bc18aea237
b9d6ce05e3e9f7572d7c627ff63065d55a873610b1fe46b6c96a386707d4c788
b9fe53d3cd2398db8ab734c6f9418f86cfa00bdd5ab00d50339a245c13821386
be1b45c1607894fd608f8a3f2075d68b278b4f0ac0c1a6df123e1582fde43adf
c1b06365cc2fa5aa50277d4bfb723abb6515435e92582144e9ff208c8be6b2e3
c224df7cafde922452b0f7dddd8e6459faffee48b19cb46ce2d0d0242ca053a9
c255693acf72b0f6d3de0b930114b0b28248cc735bae28cf882de75967d4ba66
c37bd01b17d46c77c441509b68bde27e8cd6d8d8f767d67a59708649e35b56fa
c393667527928f97793fc1ae916eeb5bb53ebfbf475acca4d7f7858a84f2807b
c479d6783f4479d3d6c4f205ff2c31b8c915cae131d7c892672cb3cb6f266803
c5ab5f8a37cdc312ebb05404fe6c193baf2fd064a9ade46f8c6d5b09bd258433
c667d1bd3d6cd0c69087f6df772bbe12837dec773e1b1a1999618c3537c2fb7b
c700c58e763a5ae34f446713819957ed9755025d35b8497ec1150f428f5ff227
c89168d63346530e40becb11bee9961f8f4ac204aa123d5ad6bc48e608ecc77d
cc07a9f0bd325aa622b9fc0f15ea34b14f61ddbfa9374e2bd91073c7ede137bd
ccc0edbb4bcec0278d2fc9fb02d8edc440152a411ad9b7de97175e5cfd917d7f
cf1fff001247fbdb3136382840a430c7c3a056d032347c0fcd7bb2d8731ff7fa
cf4724b2f736ed1a0ae6bc28f1ead963d9cd2c1fd87b6ef32e7799fc1c5c8bda
d0bffc7261df1454c5e05475cda7d9e6647318dc6c3936767e1252bfe8849c54
d2fdf0ea6e97d087e55c19447a2a212ab027724b8a731e1878c567d8c1b51394
d3f37669da130981cc76d2dcefb22a38de82ee6e0fb105b07facebcd7f4eddbc
d456c1206018ff3e37711aa22b2118e5f9f9985be3e7fc9567cb76e02c4e3501
d7d5e54ad1e33d7ab49c664323ced79cb9723ff15e9764cd0edc3e15208e8336
d961b08e4321250926de6f79087594975fe20ad1518de8f91eb711af5d1a6ef8
d9647ecef74eb4b95dee684b8e64f746c1cc25531507fdc230323944ca3a5acd
dd10579531923f3143b13c06cc3aaadf7af3d9df1c20eb83dc50e7b63518758f
dd4505c10dcc23ccb77ebee92ca3fbe0a8e57a352fcda6c2a7a780cca27b9370
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
e8e0579f3cea977b499274b637aac97822de6f09f81f244bb2022c7a015289b4
e92af41ea36051ffe9f3c83abec97cec2ac09cdaa2396863958e8b4bc8de5870
edff9075e321b40bdc5088b710519747dff0d355e2267be8fd12ffb956d03847
ee5ca5fa7137814c3b2232b406f0bf9d473dcaaaf29949835a4b221ec97c602d
eeaf94da90366254c9bd9e785dd8885dc14eb2802b41626208d111aea09c8fdb
eed0dc1fdb5d97ed188ae16fd5e1024a5bb744af47340346be2146300a6c54b9
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
eff5a4b24cdbdc1f0ce7c7619eef45d704bf196d6583499ce9d5e242dd57dfa9
f105d3d584b05d6d793ab6a36fb095095939320f95c68802513f46638cb5783d
f1a61277e3f902f50ab42015d8b07218db9b7601bb0967e54a52bfdcb4fa7e81
f318f161fb4354b77bc6a4f6086f1312b5da3991aab2668ed6e993d166928d14
f4e2021ab2924dbb4a8604e09b90b0480dcb5d855df6f95ceb88cd0b6011e6ce
f6cf1bb42463700483b7472989d3aae6d0005ae0d7548290e4a920bb0216c0e2
f782c5428289f6ae64a1aa7a4572b56bdc0b607ce9b1a979396a4e7b8f6dfd9e
fb5290615c75705d27dded2a331aac90e6c5eabba48941bbd78b52c3af158975
fbc67f7bea33a2ee53e323413356f14a4b5071afab74154afab744a1ccaaa40c
fcd1c1681d6488b333808eacb9b6941182e5ddb72aebb063d107b9ebde67b17e
fd6abf9e359db95ceba2295b57c529f60a6280d6c0be29e0636f763e6f7d6a09
ff591a993bfb2d313dd189d15d4a535fe09649178ea2b24620bb4c474be5ba87
ffcffbf74e967c947fe558fc18e1e185f9528c93cf7ca606583b9e7dd2f19bcc