
www.saipem.com
104.82.107.192
Public Scan
Open in
urlscan Pro
https://www.saipem.com/en/mail-disclaimer 11yr old
Submission: On September 15 via api (September 15th 2026, 11:05:51 am UTC) from ID — Scanned from DE Go Pro
Only in urlscan Pro
- Select different country locations for Private Scans.
- Use a global network of additional scanning locations and residential IPs for scanning.
- Interact with pages while you are scanning them.
- Download files from remote websites.
- Scan websites on the Tor Network.
Summary
TLS certificate: Issued by GeoTrust TLS RSA CA G1 on December 19th 2025. Valid for: 1yr.
This is the only time www.saipem.com was scanned on urlscan.io!
urlscan.io Verdict: No classification
Domain & IP information
| IP Address | AS Autonomous System | ||
|---|---|---|---|
| 33 | 104.82.107.192 104.82.107.192 | 16625 (AKAMAI-AS) (AKAMAI-AS - Akamai Technologies) | |
| 3 | 104.17.25.14 104.17.25.14 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 2 | 2606:4700:303... 2606:4700:3036::6815:1b98 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 2001:ad0:1000... 2001:ad0:1000:1000::148 | 3327 (CITIC CIT...) (CITIC CITIC Telecom CPC Netherlands B.V.) | |
| 5 | 2606:4700::68... 2606:4700::6812:992 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 2a02:26f0:b70... 2a02:26f0:b700:196::11a6 | 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.) | |
| 2 | 20.93.211.47 20.93.211.47 | 8075 (MICROSOFT...) (MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation) | |
| 1 | 2a02:26f0:b70... 2a02:26f0:b700:28e::11a6 | 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.) | |
| 2 | 2603:1020:203... 2603:1020:203:3::489 | 8075 (MICROSOFT...) (MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation) | |
| 50 | 9 |
ASN16625 (AKAMAI-AS - Akamai Technologies, Inc., US)
PTR: a104-82-107-192.deploy.static.akamaitechnologies.com
| www.saipem.com 11yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| cdnjs.cloudflare.com 13yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| use.fontawesome.com 10yr old |
ASN3327 (CITIC CITIC Telecom CPC Netherlands B.V., NL)
| tools.eurolandir.com 9yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| js.sitesearch360.com 5yr old | |
| cdn.sitesearch360.com 8yr old | |
| insights.sitesearch360.com 8yr old |
ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL)
| s.go-mpulse.net 9yr old |
ASN8075 (MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation, US)
| saipem.containers.piwik.pro 3yr old |
ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL)
| c.go-mpulse.net 11yr old |
ASN8075 (MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation, US)
| saipem.containers.piwik.pro 3yr old | |
| saipem.piwik.pro 3yr old |
| Apex Domain Subdomains |
Transfer | |
|---|---|---|
| 33 |
saipem.com
www.saipem.com 11yr old |
1 MB |
| 5 |
sitesearch360.com
js.sitesearch360.com — Cisco Umbrella Rank: 204447 5yr old cdn.sitesearch360.com — Cisco Umbrella Rank: 137918 8yr old insights.sitesearch360.com — Cisco Umbrella Rank: 134626 8yr old |
128 KB |
| 4 |
piwik.pro
saipem.containers.piwik.pro 3yr old saipem.piwik.pro 3yr old |
112 KB |
| 3 |
cloudflare.com
cdnjs.cloudflare.com — Cisco Umbrella Rank: 384 13yr old |
273 KB |
| 2 |
go-mpulse.net
s.go-mpulse.net — Cisco Umbrella Rank: 2238 9yr old c.go-mpulse.net — Cisco Umbrella Rank: 1478 11yr old |
56 KB |
| 2 |
fontawesome.com
use.fontawesome.com — Cisco Umbrella Rank: 2074 10yr old |
620 KB |
| 1 |
eurolandir.com
tools.eurolandir.com — Cisco Umbrella Rank: 152481 9yr old |
3 KB |
| 50 | 7 |
| Domain | Requested by | |
|---|---|---|
| 33 | www.saipem.com |
www.saipem.com
|
| 3 | cdn.sitesearch360.com |
js.sitesearch360.com
cdn.sitesearch360.com |
| 3 | saipem.containers.piwik.pro |
www.saipem.com
saipem.containers.piwik.pro |
| 3 | cdnjs.cloudflare.com |
www.saipem.com
cdnjs.cloudflare.com |
| 2 | use.fontawesome.com |
www.saipem.com
|
| 1 | saipem.piwik.pro |
saipem.containers.piwik.pro
|
| 1 | c.go-mpulse.net |
s.go-mpulse.net
|
| 1 | insights.sitesearch360.com |
cdn.sitesearch360.com
|
| 1 | s.go-mpulse.net |
www.saipem.com
|
| 1 | js.sitesearch360.com |
www.saipem.com
|
| 1 | tools.eurolandir.com |
www.saipem.com
|
| 50 | 11 |
This site contains links to these domains. Also see Links.
| Domain |
|---|
| saipem.sharepoint.com |
| www.linkedin.com |
| www.instagram.com |
| www.youtube.com |
| vendor.supplhi.com |
| Subject Issuer | Validity | Valid | |
|---|---|---|---|
| www.saipem.com GeoTrust TLS RSA CA G1 |
2025-12-19 - 2026-12-18 |
1yr | crt.sh |
| cdnjs.cloudflare.com WE1 |
2026-09-07 - 2026-12-06 |
3mo | crt.sh |
| use.fontawesome.com WE1 |
2026-08-19 - 2026-11-17 |
3mo | crt.sh |
| *.eurolandir.com GlobeSSL DV CA |
2025-12-08 - 2027-01-01 |
1yr | crt.sh |
| sitesearch360.com WE1 |
2026-08-22 - 2026-11-20 |
3mo | crt.sh |
| akstat.io DigiCert Global G3 TLS ECC SHA384 2020 CA1 |
2026-04-30 - 2026-11-14 |
7mo | crt.sh |
| *.containers.piwik.pro GlobeSSL DV CA |
2025-12-03 - 2027-01-01 |
1yr | crt.sh |
| *.piwik.pro GlobeSSL DV CA |
2025-12-03 - 2027-01-03 |
1yr | crt.sh |
This page contains 1 frames:
Primary Page:
https://www.saipem.com/en/mail-disclaimer
Frame ID: E648E56EFD5DE2A2AA1078E2D7B6DF9A
Requests: 50 HTTP requests in this frame
Screenshot
Go Pro
Only in urlscan Pro
Use the Visual Search feature to find pages with visually similar screenshots.
Click for more information
Free trials of urlscan Pro are available.
Page Title
mail-disclaimer | SaipemDetected technologies
 Drupal
(CMS)
Expand
Detected patterns
- drupal\.js
 Bootstrap
(UI frameworks)
Expand
Detected patterns
- (?:/|-)bootstrap(?:[^/]*?([0-9a-fA-F]{7,40}|[\d]+(?:\.[\d]+(?:\.[\d]+)?)?)|)[^/]*?(?:\.min)?\.js
 cdnjs
(CDN)
Expand
Detected patterns
- cdnjs\.cloudflare\.com
 Font Awesome
(Font scripts)
Expand
Detected patterns
- (?:F|f)o(?:n|r)t-?(?:A|a)wesome(?:.*?([0-9a-fA-F]{7,40}|[\d]+(?:.[\d]+(?:.[\d]+)?)?)|)
 jQuery
(JavaScript libraries)
Expand
Detected patterns
- jquery
 Piwik PRO Core
(Analytics)
Expand
Detected patterns
- \.piwik\.pro/
Page Statistics
5 Outgoing links
Go Pro
Only in urlscan Pro
Effortlessly use any on-page link as a pivot to discover other pages pointing to the exact same destination. Seamlessly trace both specific URLs and broader domains to uncover hidden connection networks and map out backlink relationships with ease.
Click for more information
Free trials of urlscan Pro are available.
These are links going to different origins than the main page.
Title: Access to the intranet portal
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Title: Qualification Management
Search URL Search Domain Scan URL
Redirected requests
There were HTTP redirect chains for the following requests:
50 HTTP transactions
Go Pro
Only in urlscan Pro
Inspect WebSocket connections, examine POST data effortlessly, and track overlap counts in real time. Features live search and filtering across all HTTP output, complete with full response metadata for deep analysis.
Click for more information
Free trials of urlscan Pro are available.
0 data transactions
| Method Protocol |
Status | Resource Path |
Size x-fer |
Time Latency |
Type MIME-Type |
IP Location |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
|
GET H/1.1 |
200 OK |
Primary Request
mail-disclaimer
Show response
www.saipem.com/en/ |
144 KB 26 KB |
245ms
122ms |
Document
text/html |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
css_7kqLZvzqoedvCFUHe0teigL8wvEXnQYJPO7WRY5S94A.css
www.saipem.com/sites/default/files/css/ |
19 KB 5 KB |
45ms
28ms |
Stylesheet
text/css |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
css_cNlihyBr3rTiwRBkYHl93gvrymS7z6n9IzJifDM82Tg.css
www.saipem.com/sites/default/files/css/ |
370 KB 53 KB |
134ms
93ms |
Stylesheet
text/css |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
all.min.css
cdnjs.cloudflare.com/ajax/libs/font-awesome/6.1.2/css/ |
99 KB 17 KB |
104ms
38ms |
Stylesheet
text/css |
104.17.25.14 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
css_jQghbB6-IvJEV0qshK_Gs8XtR4xBOt1i0rmIby9ONPE.css
www.saipem.com/sites/default/files/css/ |
667 KB 76 KB |
402ms
363ms |
Stylesheet
text/css |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
all.js
Show response
use.fontawesome.com/releases/v6.1.0/js/ |
2 MB 611 KB |
97ms
35ms |
Script
application/javascript |
2606:4700:3036::6815:1b98 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
v4-shims.js
Show response
use.fontawesome.com/releases/v6.1.0/js/ |
26 KB 8 KB |
86ms
24ms |
Script
application/javascript |
2606:4700:3036::6815:1b98 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
/
tools.eurolandir.com/tools/ticker/ |
2 KB 3 KB |
1493ms
463ms |
Image
image/png |
2001:ad0:1000:1000::148 CITIC CITIC Telec... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
jquery.min.js
Show response
www.saipem.com/core/assets/vendor/jquery/ |
85 KB 30 KB |
368ms
337ms |
Script
text/javascript |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
once.min.js
Show response
www.saipem.com/core/assets/vendor/once/ |
1 KB 1 KB |
33ms
32ms |
Script
text/javascript |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
drupalSettingsLoader.js
Show response
www.saipem.com/core/misc/ |
691 B 817 B |
268ms
267ms |
Script
text/javascript |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
drupal.js
Show response
www.saipem.com/core/misc/ |
21 KB 6 KB |
37ms
37ms |
Script
text/javascript |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
drupal.init.js
Show response
www.saipem.com/core/misc/ |
960 B 920 B |
253ms
253ms |
Script
text/javascript |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
index.umd.min.js
Show response
www.saipem.com/core/assets/vendor/tabbable/ |
6 KB 3 KB |
47ms
43ms |
Script
text/javascript |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
bootstrap.bundle.js
Show response
www.saipem.com/themes/contrib/bootstrap5/dist/bootstrap/5.3.6/dist/js/ |
203 KB 44 KB |
39ms
35ms |
Script
text/javascript |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
scripts.js
Show response
www.saipem.com/themes/custom/saipem_theme/dist/js/ |
360 KB 105 KB |
46ms
42ms |
Script
text/javascript |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
progress.js
Show response
www.saipem.com/core/misc/ |
5 KB 2 KB |
30ms
27ms |
Script
text/javascript |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
loadjs.min.js
Show response
www.saipem.com/core/assets/vendor/loadjs/ |
2 KB 1 KB |
68ms
26ms |
Script
text/javascript |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
debounce.js
Show response
www.saipem.com/core/misc/ |
1 KB 1 KB |
52ms
34ms |
Script
text/javascript |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
announce.js
Show response
www.saipem.com/core/misc/ |
4 KB 2 KB |
32ms
31ms |
Script
text/javascript |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
message.js
Show response
www.saipem.com/core/misc/ |
8 KB 3 KB |
32ms
32ms |
Script
text/javascript |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
ajax.js
Show response
www.saipem.com/core/misc/ |
65 KB 17 KB |
73ms
73ms |
Script
text/javascript |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
ultimenu.base.min.js
Show response
www.saipem.com/modules/contrib/ultimenu/js/ |
4 KB 2 KB |
42ms
42ms |
Script
text/javascript |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
ultimenu.min.js
Show response
www.saipem.com/modules/contrib/ultimenu/js/ |
751 B 833 B |
41ms
40ms |
Script
text/javascript |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
ultimenu.ajax.min.js
Show response
www.saipem.com/modules/contrib/ultimenu/js/ |
621 B 820 B |
30ms
30ms |
Script
text/javascript |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
8973.js
Show response
js.sitesearch360.com/plugin/bundle/ |
3 KB 2 KB |
132ms
71ms |
Script
application/javascript |
2606:4700::6812:992 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
dropbutton.js
Show response
www.saipem.com/core/misc/dropbutton/ |
6 KB 2 KB |
26ms
25ms |
Script
text/javascript |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
46BG7-YCFJY-WU2YT-ZMEJK-J924Z
Show response
s.go-mpulse.net/boomerang/ |
205 KB 56 KB |
144ms
33ms |
Script
application/javascript |
2a02:26f0:b700:196::11a6 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
93fbd86b-b1bc-41a9-9e3b-46192e5a79c5.js
Show response
saipem.containers.piwik.pro/ |
246 KB 72 KB |
409ms
51ms |
Script
application/javascript |
20.93.211.47 Microsoft Corpora... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
icon-dark-blue.svg
www.saipem.com/themes/custom/saipem_theme/dist/images/ |
233 B 593 B |
95ms
30ms |
Image
image/svg+xml |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
search-icon.svg
www.saipem.com/modules/custom/saipem_sitesearch/img/ |
315 B 633 B |
350ms
253ms |
Image
image/svg+xml |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
AktivGrotesk_Rg.ttf
www.saipem.com/themes/custom/saipem_theme/dist/fonts/ |
377 KB 186 KB |
368ms
359ms |
Font
font/ttf |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
AktivGrotesk_Bd.ttf
www.saipem.com/themes/custom/saipem_theme/dist/fonts/ |
376 KB 184 KB |
148ms
130ms |
Font
font/ttf |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
BlenderPro-Bold.ttf
www.saipem.com/themes/custom/saipem_theme/dist/fonts/ |
127 KB 56 KB |
79ms
53ms |
Font
font/ttf |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
BlenderPro-Medium.otf
www.saipem.com/themes/custom/saipem_theme/dist/fonts/ |
60 KB 60 KB |
200ms
159ms |
Font
font/otf |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
fa-solid-900.woff2
cdnjs.cloudflare.com/ajax/libs/font-awesome/6.1.2/webfonts/ |
151 KB 152 KB |
97ms
95ms |
Font
application/octet-stream |
104.17.25.14 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
overrides-logo-colored.svg
www.saipem.com/themes/custom/saipem_theme/ |
3 KB 2 KB |
201ms
29ms |
Image
image/svg+xml |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
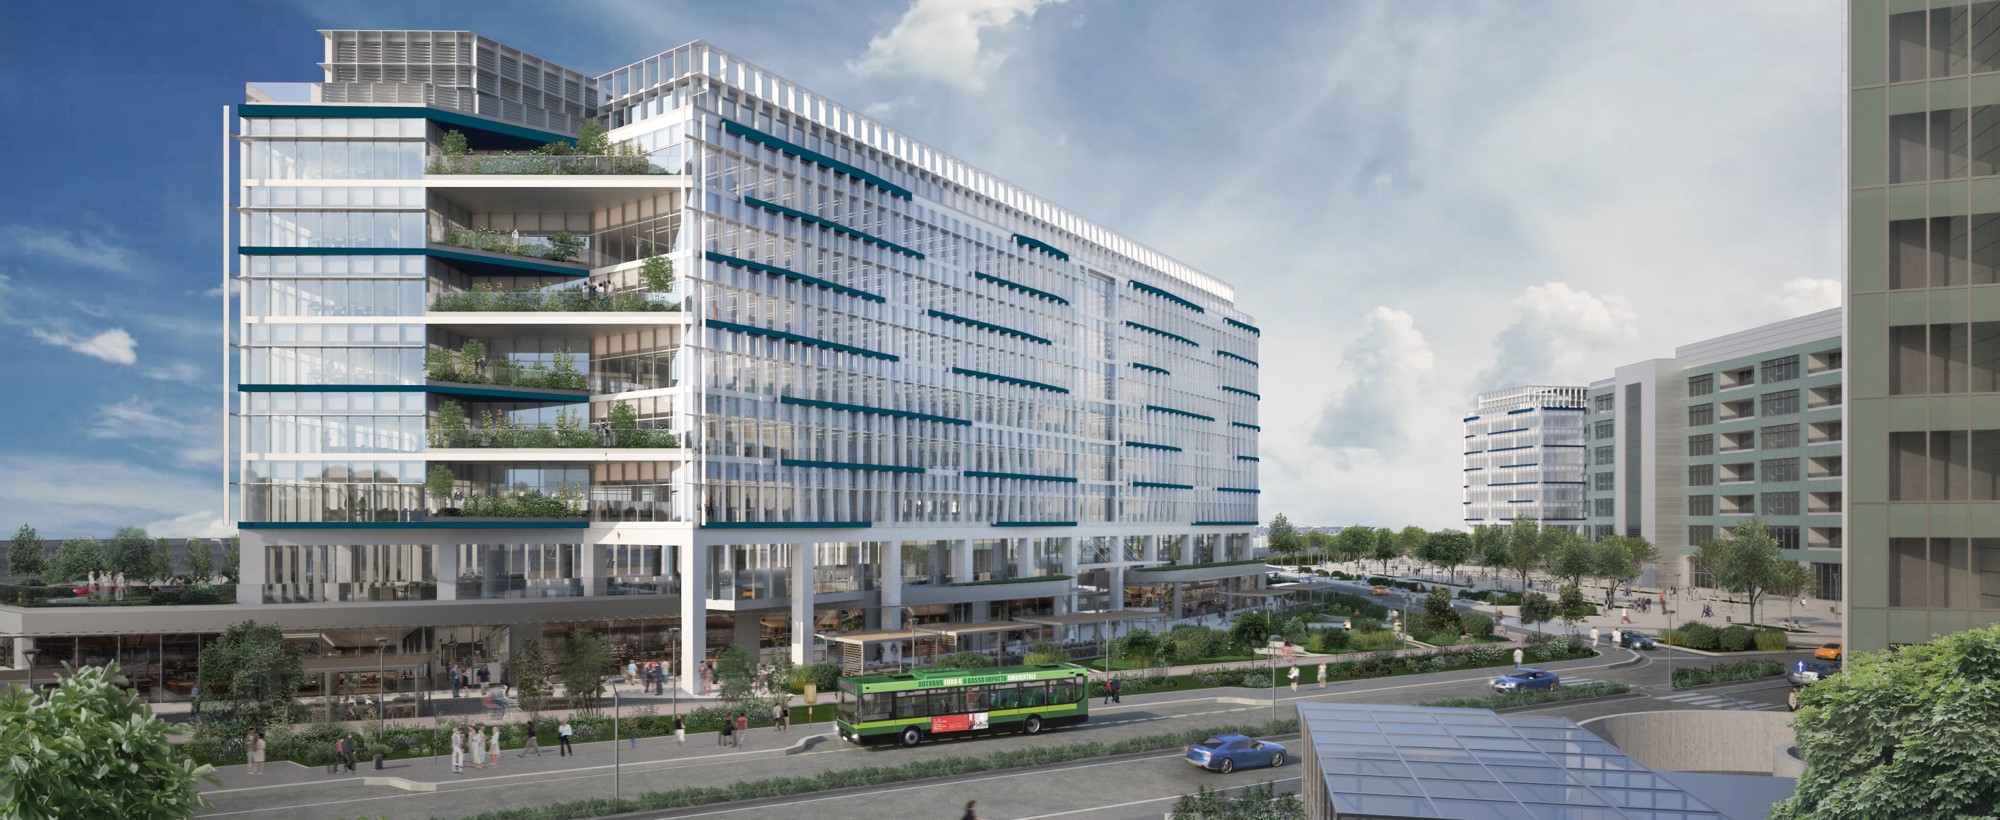
Vista%20facciata%20Sud%20Est%20edificio%20Spark%20One.jpg
www.saipem.com/sites/default/files/2023-06/ |
395 KB 396 KB |
158ms
77ms |
Image
image/jpeg |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
fa-brands-400.woff2
cdnjs.cloudflare.com/ajax/libs/font-awesome/6.1.2/webfonts/ |
103 KB 103 KB |
73ms
73ms |
Font
application/octet-stream |
104.17.25.14 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
overrides-logo.svg
www.saipem.com/themes/custom/saipem_theme/ |
3 KB 1 KB |
108ms
108ms |
Image
image/svg+xml |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
award.png
www.saipem.com/sites/default/files/inline-images/ |
19 KB 19 KB |
400ms
398ms |
Image
image/png |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
sitesearch360-v14.frozen.021e55da7c3c18ad2ad0075756a74437.js
Show response
cdn.sitesearch360.com/v14/ |
337 KB 100 KB |
27ms
15ms |
Script
application/javascript |
2606:4700::6812:992 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
session
Show response
insights.sitesearch360.com/insights/ |
0 188 B |
345ms
83ms |
XHR
text/plain |
2606:4700::6812:992 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
ss360-unibox-v14.chunk.f4c74eca30d264a93aa3.js
Show response
cdn.sitesearch360.com/v14/ |
56 KB 15 KB |
295ms
251ms |
Script
application/javascript |
2606:4700::6812:992 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
ss360-styles-v14.chunk.8afa7fc4ce44fc8d4319.js
Show response
cdn.sitesearch360.com/v14/ |
57 KB 12 KB |
332ms
289ms |
Script
application/javascript |
2606:4700::6812:992 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
config.json
Show response
c.go-mpulse.net/api/ |
49 B 212 B |
746ms
416ms |
XHR
application/json |
2a02:26f0:b700:28e::11a6 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
privacy-widgets.json
Show response
saipem.containers.piwik.pro/93fbd86b-b1bc-41a9-9e3b-46192e5a79c5/ |
104 KB 14 KB |
336ms
42ms |
XHR
application/json |
2603:1020:203:3::489 Microsoft Corpora... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
ppms.js
Show response
saipem.containers.piwik.pro/ |
67 KB 26 KB |
117ms
117ms |
Script
application/javascript |
20.93.211.47 Microsoft Corpora... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
202 |
ppms.php
saipem.piwik.pro/ |
0 0 |
69ms
22ms |
Ping
text/html |
2603:1020:203:3::489 Microsoft Corpora... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
favicon.ico
www.saipem.com/themes/custom/saipem_theme/ |
15 KB 2 KB |
31ms
31ms |
Other
image/vnd.microsoft.icon |
104.82.107.192 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||








Verdicts & Comments Add Verdict or Comment
44 JavaScript Window variables
Go Pro
Only in urlscan Pro
Inspect and pivot on JavaScript variables, identifiers, and other key site metadata data with urlscan Pro. Reveal and search on client-side frameworks, runtime variables, and custom values.
Click for more information
Free trials of urlscan Pro are available.
These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.
string| BOOMR_API_key object| BOOMR object| dataLayer object| ppms function| jQuery function| once object| drupalSettings object| Drupal object| tabbable number| uidEvent object| bootstrap object| webpackChunksaipem_theme boolean| VimeoPlayerResizeEmbeds_ boolean| VimeoSeoMetadataAppended function| loadjs object| ss360Config object| webpackChunksitesearch360_js object| __ss360CallbacksMap function| sxQuery function| initializeSs360 object| SS360Insights boolean| _ss360_keydown.ss360TrackingDisabler object| SS360 boolean| _ss360_popstate.ss360History boolean| _ss360_resize.ss360ApplyStyles boolean| _ss360_orientationchange.ss360ApplyStyles function| BOOMR_check_doc_domain object| ErrorStackParser object| UserTimingCompression object| BOOMR_mq object| sevenTag object| wgxpath object| _paq boolean| _ss360_resize object| ___FONT_AWESOME___ object| FontAwesomeConfig object| FontAwesome object| a object| fontawesome-free-shims object| Piwik object| AnalyticsTracker function| piwik_log number| BOOMR_onload number| BOOMR_configt5 Cookies
Go Pro
Only in urlscan Pro
Review, search, and pivot on browser cookies and persistence site data to see how a site tracks users and keeps sessions alive across visits.
Click for more information
Free trials of urlscan Pro are available.
Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.
| Domain/Path | Expires | Name / Value | |||
|---|---|---|---|---|---|
| www.saipem.com/ | 1970-01-22 01:50:06 |
Name: ssi--sessionId Value: 4cdf827e-76d1-311d-46c4-9306256fb54f |
|||
| www.saipem.com/ | 1970-01-21 17:04:30 |
Name: ssi--lastInteraction Value: 1789470353574 |
|||
| www.saipem.com/ | 1970-01-21 17:04:32 |
Name: _pk_id.93fbd86b-b1bc-41a9-9e3b-46192e5a79c5.cc7f Value: 9eb955cf7e52e470.1789470354.1.1789470354.. |
|||
| www.saipem.com/ | 1970-01-21 17:04:32 |
Name: _pk_ses.93fbd86b-b1bc-41a9-9e3b-46192e5a79c5.cc7f Value: * |
|||
| .saipem.com/ | 1970-01-21 17:14:35 |
Name: RT Value: "z=1&dm=saipem.com&si=c5350511-06a7-4cf2-9f93-7a9231359b2b&ss=mu2kg0bz&sl=1&tt=1sj&rl=1&ld=251" |
Security Headers
This page lists any security headers set by the main page. If you want to understand what these mean and how to use them, head on over to this page
| Header | Value |
|---|---|
| Content-Security-Policy | default-src * 'strict-dynamic'; font-src 'self' cdnjs.cloudflare.com; frame-src *; img-src * data:; object-src 'self' *.saipem.com; script-src 'self' 'strict-dynamic' *.piwik.com google.com gstatic.com www.google.com cdn.datatables.net cdnjs.cloudflare.com https://cdn.jsdelivr.net https://cdnjs.cloudflare.com https://js.sitesearch360.com https://saipem-cdn.thron.com https://unpkg.com https://use.fontawesome.com https://www.google.com unpkg.com www.gstatic.com; script-src-attr 'self' 'unsafe-inline'; script-src-elem 'self' 'unsafe-inline' www.google.com google.com gstatic.com *.piwik.com saipem.containers.piwik.pro cdn.sitesearch360.com s.go-mpulse.net *.youtube.com cdn.datatables.net cdnjs.cloudflare.com https://cdn.jsdelivr.net https://cdnjs.cloudflare.com https://js.sitesearch360.com https://saipem-cdn.thron.com https://unpkg.com https://use.fontawesome.com https://www.google.com unpkg.com www.gstatic.com; style-src 'self' 'unsafe-inline' cdn.datatables.net https://cdn.jsdelivr.net https://cdnjs.cloudflare.com https://unpkg.com unpkg.com; style-src-attr 'unsafe-inline'; frame-ancestors *; report-uri https://www.saipem.com/en/report-uri/enforce; upgrade-insecure-requests |
| X-Content-Type-Options | nosniff |
| X-Frame-Options | SAMEORIGIN |
Indicators
This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.
c.go-mpulse.net
cdn.sitesearch360.com
cdnjs.cloudflare.com
insights.sitesearch360.com
js.sitesearch360.com
s.go-mpulse.net
saipem.containers.piwik.pro
saipem.piwik.pro
tools.eurolandir.com
use.fontawesome.com
www.saipem.com
104.17.25.14
104.82.107.192
20.93.211.47
2001:ad0:1000:1000::148
2603:1020:203:3::489
2606:4700:3036::6815:1b98
2606:4700::6812:992
2a02:26f0:b700:196::11a6
2a02:26f0:b700:28e::11a6
088e8584451c206d587b683dbc1b68cfbd05d02761f6c4709083f29cc11b5a6b
08917ce03bf43e31f728f6aa830cd2f8d252e39a8f6d769578f07b500c3eb87f
09ebd7f407439990aac227e70da23e1a819e8e30282928e324370805f480bec4
0a61dec2fd3d6d4fb688c4d0500f5f6268147c6771f2fe9e095d1cd074ca56fd
1c6fbe8e338e42b3cc41f383f5dae2c304b4db5471a9f48911d6a6ba3a35c9c2
1d137f9b816994ff3dd240ef04942ebf47c48131c32b0acc640db3065755d496
1e62a545e1180a257d1a77e1c55f355ae5ea309ea2e82244420609af395746dc
1ecf4736bd6abe2ecee8d3a7b35266c04d96db7c91dc2d2990e4c9c5f10a800e
2ccb66eceb05e6d15ca71a6605ec4e75dbb7d25f97cfe15409204fa2f7e212df
3587424d56f106709ced9ab246f44eccef6ad8d1e39e85ab332c48758f864a29
3662cdd25882ca849ea513c2b0b0b9ec3cb56385761c0c6dfd7d12aa1ec055be
4485ca40b5215a24b35262cc241e42172978f03f3817d15c1f6633aa12db8503
4cffbb39def2c81edc6291cbe27d638c94dea87674f19bc3ea03c6c14a729573
50a4fbfb49d24895778871fd8217ee6874ad1abc6d39d385e6f6849970db1a29
52bbd916956b4ed8b9d71d1784e4008b207814ec506203326fb36052f3451adb
58cae60e9b4fe52945838f8193b1dfa003b49f7d8c2864c4ee11aad039819027
5a469fe297b6aa0a085516fd4888b7a3e64deca17c35ccbe73842003c8128a48
68d6e536e28671d95ee7fdb6dd5a4f046d6a49f9f916e2d2d3992c4120268b43
6e8066fd6068068986e5430de16fdaa63693cb6be6f2addc34dfd66d33c231b9
741e3e952a8b5c4f21aab2d5a2717535b4e4ca6d59b3af634a1d334f3280f59a
86410e06a0c63da0a1a6d996b5ba3366f0a9ee9f2d3219636beb933a0ec364fb
86fd0c2f616cb18d9f55832633e093597bd2c6ea8530c2ee2256f2ae55c8a4c4
923935d813106205b31d3953b21e34a007f32758ec0c3d2ba6dd3dda1f8cf6e9
967394d1fd10b388d99bec9df2a3cab546a40f695f5c70641daf0b51af5604c6
a1967ea12d2d1c1d3b6665ed2795e4e82d855089059777cefaa07a60481ae86d
a265a819c15fbbc36d727876d465f57091eba5bc22531b6c411fab94fae13d63
a4c4c16266afbf15b07a0ceac0998c9a66152ec437731896062f72abf771ccd3
a7275ddf5a9e695c2767bce654564447b45db2561349ae0bd3967de818f4ae90
a73d4637fbd5f18d34fdd3a72a8b75a9e588207feae1218334c35f369673c9c9
a7c3958bb3359d5c8879270491b08a1fbc21e6575a35134c8f9354f4d8b0074a
ab763556dbbedc5b4a3d861b696908905ff1cda75b7012f3ea9554386e005dc6
b2b6719be817e44047b0ed480d714617a663cb3b90b87751a76757818525e289
bbe2ceb0b5b4002315f9da4d02e97fbd78bf0ef9be4f5daf6949a37a5c2ccfad
bd447ec448a3bb2a43ba3adb54d13cf8c7d4465c15ee403ce26519c975bc0852
c1cda5cee856901b610650602379500378b74e7300d04dca5f9dc87f2e20a210
c5e8e8eb22e2eaf1ad02370c22c63c04774ab0b83b4329d5945333750814bb2f
cb544b834006e9477065397c2817317a877374e03e341b1c73f8e5e54aa81c76
cb726792234baef8c90f596588c3778409ec49155fcece0ddc2437ec9026cb2f
d2a8c23d519d1d8e468d38d246b93e8d9ebef4a91b5ea18b71b924915436668d
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
e4f48e1f5558252eba1d25be60a35a35a024390cf4970e0652b9e654f9e0302b
e898e859992ccdbd321b368e60bc8ba002f8fc71a43fd5dedbdd5597f4d005ae
ecb9adac3f64c56265e564cf8da2d813bcf55a2f61df15936f4c258cc13c856f
f0652db907b00de7d169ef99f6fb3cbd7e35c55ee448e0be23704e65a9778b6d
f1f61749d900987a32e63f8e947c47daf54b1fee7c6cc1e12ff07cdb19b5856a
f47d56f4e42a0fd576ee274454e24c085010b464b849cabe80041c88aaf45363
f5dfe5161b8675fc999a37f8af7a0920a0ac077c2531288cc0549d6049d4ff90
f845561c9619e20d0514a0fb5bc4b4e12b5edca0460c822ea1f34996084fc7c6
fc9a93dd241f6b045cbff0481cf4e1901becd0e12fb45166a8f17f95823f0b1a