Summary

This website contacted 109 IPs in 13 countries across 98 domains to perform 335 HTTP transactions. The main IP is 77.79.221.168, located in Wieliszew, Poland and belongs to ATMAN-ISP-AS Atman Sp. z o.o., PL. The main domain is sklep.doppelherz.pl. 4yr old
TLS certificate: Issued by Shoper DV TLS G2 R34 CA on May 18th 2026. Valid for: 7mo.
This is the only time sklep.doppelherz.pl was scanned on urlscan.io!

Domain & IP information

IP Address AS Autonomous System
69 77.79.221.168 77.79.221.168 15694 (ATMAN-ISP...) (ATMAN-ISP-AS Atman Sp. z o.o.)
1 104.26.10.75 104.26.10.75 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
3 95.131.136.1 95.131.136.1 8426 (CLARANET-...) (CLARANET-AS Claranet Limited)
1 3.174.46.3 3.174.46.3 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
19 54.192.35.76 54.192.35.76 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 104.17.24.14 104.17.24.14 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
2 142.251.14.101 142.251.14.101 15169 (GOOGLE) (GOOGLE - Google LLC)
4 65.8.131.85 65.8.131.85 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 18.198.138.71 18.198.138.71 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
6 192.178.183.97 192.178.183.97 15169 (GOOGLE) (GOOGLE - Google LLC)
1 185.31.26.219 185.31.26.219 42656 (QXL-POLAN...) (QXL-POLAND Allegro sp. z o.o.)
6 212.77.113.26 212.77.113.26 12827 (Wirtualna...) (WirtualnaPolska Wirtualna Polska Media S.A.)
6 142.251.156.4 142.251.156.4 15169 (GOOGLE) (GOOGLE - Google LLC)
1 185.41.71.25 185.41.71.25 50840 (AS-HITME ...) (AS-HITME Marek Bajerski trading as HITME.PL)
2 185.41.68.192 185.41.68.192 50840 (AS-HITME ...) (AS-HITME Marek Bajerski trading as HITME.PL)
3 172.64.146.195 172.64.146.195 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
7 195.181.175.40 195.181.175.40 60068 (CDN77 Dat...) (CDN77 Datacamp Limited)
4 142.251.14.95 142.251.14.95 15169 (GOOGLE) (GOOGLE - Google LLC)
9 192.178.183.94 192.178.183.94 15169 (GOOGLE) (GOOGLE - Google LLC)
1 2 142.251.14.156 142.251.14.156 15169 (GOOGLE) (GOOGLE - Google LLC)
1 142.251.20.148 142.251.20.148 15169 (GOOGLE) (GOOGLE - Google LLC)
9 142.251.157.119 142.251.157.119 15169 (GOOGLE) (GOOGLE - Google LLC)
3 212.77.113.48 212.77.113.48 12827 (Wirtualna...) (WirtualnaPolska Wirtualna Polska Media S.A.)
1 212.77.98.32 212.77.98.32 12827 (Wirtualna...) (WirtualnaPolska Wirtualna Polska Media S.A.)
1 142.251.110.119 142.251.110.119 15169 (GOOGLE) (GOOGLE - Google LLC)
5 216.239.32.36 216.239.32.36 15169 (GOOGLE) (GOOGLE - Google LLC)
2 142.251.14.113 142.251.14.113 15169 (GOOGLE) (GOOGLE - Google LLC)
1 54.192.35.44 54.192.35.44 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 46.137.100.189 46.137.100.189 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 37.157.4.21 37.157.4.21 198622 (ADFORM Ad...) (ADFORM Adform A/S)
3 142.132.237.132 142.132.237.132 24940 (HETZNER-A...) (HETZNER-AS Hetzner Online GmbH)
1 104.26.0.138 104.26.0.138 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
1 142.251.20.156 142.251.20.156 15169 (GOOGLE) (GOOGLE - Google LLC)
2 172.217.116.4 172.217.116.4 15169 (GOOGLE) (GOOGLE - Google LLC)
2 81.17.55.173 81.17.55.173 60781 (LEASEWEB-...) (LEASEWEB-NL-AMS-01 LeaseWeb Netherlands B.V.)
7 8 142.251.110.154 142.251.110.154 15169 (GOOGLE) (GOOGLE - Google LLC)
1 10 37.157.2.13 37.157.2.13 198622 (ADFORM Ad...) (ADFORM Adform A/S)
1 3 104.18.27.193 104.18.27.193 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
2 103.231.98.109 103.231.98.109 62713 (AS-PUBMATIC) (AS-PUBMATIC - PubMatic)
2 18.200.137.183 18.200.137.183 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 51.77.41.26 51.77.41.26 16276 (OVH OVH SAS) (OVH OVH SAS)
2 91.216.25.161 91.216.25.161 196899 (Integer I...) (Integer INTEGER.pl S.A.)
2 146.59.84.109 146.59.84.109 16276 (OVH OVH SAS) (OVH OVH SAS)
2 34.249.139.175 34.249.139.175 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 49.12.245.74 49.12.245.74 24940 (HETZNER-A...) (HETZNER-AS Hetzner Online GmbH)
1 34.117.39.58 34.117.39.58 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC)
1 172.67.159.95 172.67.159.95 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
2 37.27.169.254 37.27.169.254 24940 (HETZNER-A...) (HETZNER-AS Hetzner Online GmbH)
2 91.134.222.90 91.134.222.90 16276 (OVH OVH SAS) (OVH OVH SAS)
1 34.159.90.131 34.159.90.131 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC)
1 99.84.152.66 99.84.152.66 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
2 172.66.166.111 172.66.166.111 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
1 37.157.4.29 37.157.4.29 198622 (ADFORM Ad...) (ADFORM Adform A/S)
2 4 192.178.183.157 192.178.183.157 15169 (GOOGLE) (GOOGLE - Google LLC)
2 104.18.31.101 104.18.31.101 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
2 52.19.173.53 52.19.173.53 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
4 52.213.207.85 52.213.207.85 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 35.242.250.78 35.242.250.78 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC)
1 54.195.115.7 54.195.115.7 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 91.134.222.93 91.134.222.93 16276 (OVH OVH SAS) (OVH OVH SAS)
1 37.157.6.246 37.157.6.246 198622 (ADFORM Ad...) (ADFORM Adform A/S)
6 77.79.221.139 77.79.221.139 15694 (ATMAN-ISP...) (ATMAN-ISP-AS Atman Sp. z o.o.)
1 34.241.233.208 34.241.233.208 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 88.221.170.40 88.221.170.40 16625 (AKAMAI-AS) (AKAMAI-AS - Akamai Technologies)
1 69.173.144.138 69.173.144.138 26667 (RUBICONPR...) (RUBICONPROJECT - Magnite)
1 18.157.227.77 18.157.227.77 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 18.134.84.75 18.134.84.75 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 35.214.136.108 35.214.136.108 15169 (GOOGLE) (GOOGLE - Google LLC)
1 2 77.243.51.121 77.243.51.121 42697 (NETIC-AS ...) (NETIC-AS Netic A/S)
1 63.183.69.9 63.183.69.9 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 34.242.143.121 34.242.143.121 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
2 2 35.244.174.68 35.244.174.68 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC)
2 15.197.193.217 15.197.193.217 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 34.254.69.83 34.254.69.83 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 35.244.159.8 35.244.159.8 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC)
1 193.135.9.133 193.135.9.133 48314 (IP-PROJEC...) (IP-PROJECTS Michael Sebastian Schinzel trading as IP-Projects GmbH & Co. KG)
1 99.84.152.34 99.84.152.34 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
2 3 34.102.136.131 34.102.136.131 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC)
2 2 54.171.79.239 54.171.79.239 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 35.167.241.13 35.167.241.13 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 85.114.159.93 85.114.159.93 24961 (MYLOC-AS ...) (MYLOC-AS WIIT AG)
2 2 35.210.130.15 35.210.130.15 15169 (GOOGLE) (GOOGLE - Google LLC)
1 135.125.170.28 135.125.170.28 16276 (OVH OVH SAS) (OVH OVH SAS)
2 2 91.216.195.30 91.216.195.30 12516 (WEBORAMA ...) (WEBORAMA WEBORAMA SA)
1 151.101.66.132 151.101.66.132 54113 (FASTLY) (FASTLY - Fastly)
1 35.214.217.206 35.214.217.206 15169 (GOOGLE) (GOOGLE - Google LLC)
1 54.36.150.186 54.36.150.186 16276 (OVH OVH SAS) (OVH OVH SAS)
2 79.137.99.232 79.137.99.232 16276 (OVH OVH SAS) (OVH OVH SAS)
1 3.120.74.76 3.120.74.76 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 46.105.34.150 46.105.34.150 16276 (OVH OVH SAS) (OVH OVH SAS)
5 51.210.24.88 51.210.24.88 16276 (OVH OVH SAS) (OVH OVH SAS)
7 99.80.34.227 99.80.34.227 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 104.18.41.61 104.18.41.61 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
11 188.114.96.3 188.114.96.3 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
4 188.114.97.3 188.114.97.3 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
1 2 82.223.103.149 82.223.103.149 8560 (IONOS-AS ...) (IONOS-AS IONOS SE)
1 212.129.3.113 212.129.3.113 12876 (AS12876 S...) (AS12876 Scaleway SAS)
3 18.197.44.30 18.197.44.30 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
2 104.18.0.2 104.18.0.2 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
2 172.67.150.171 172.67.150.171 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
1 78.46.234.191 78.46.234.191 24940 (HETZNER-A...) (HETZNER-AS Hetzner Online GmbH)
3 34.102.157.203 34.102.157.203 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC)
2 104.21.10.19 104.21.10.19 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
1 34.149.104.117 34.149.104.117 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC)
1 51.38.158.176 51.38.158.176 16276 (OVH OVH SAS) (OVH OVH SAS)
1 3.131.73.36 3.131.73.36 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 216.239.36.21 216.239.36.21 15169 (GOOGLE) (GOOGLE - Google LLC)
5 85.195.93.95 85.195.93.95 29066 (VELIANET-...) (VELIANET-AS velia.net Internetdienste GmbH)
1 85.195.73.74 85.195.73.74 29066 (VELIANET-...) (VELIANET-AS velia.net Internetdienste GmbH)
1 104.18.2.89 104.18.2.89 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
1 92.113.16.12 92.113.16.12 47583 (AS-HOSTIN...) (AS-HOSTINGER Hostinger International Limited)
2 104.18.41.22 104.18.41.22 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
335 109
Apex Domain
Subdomains
Transfer
73 doppelherz.pl
sklep.doppelherz.pl 4yr old
dfd.doppelherz.pl 4yr old
tagmanager.sklep.doppelherz.pl 1yr old
3 MB
20 trustmate.io
trustmate.io — Cisco Umbrella Rank: 173668 8yr old
papi.trustmate.io — Cisco Umbrella Rank: 602312 4yr old
356 KB
14 doofinder.com
eu1-config.doofinder.com — Cisco Umbrella Rank: 51914 2yr old
cdn.doofinder.com — Cisco Umbrella Rank: 32397 10yr old
eu1-search.doofinder.com — Cisco Umbrella Rank: 61724 10yr old
eu1-recommendations.doofinder.com — Cisco Umbrella Rank: 265194 2yr old
eu1-api.doofinder.com — Cisco Umbrella Rank: 46795 2yr old
147 KB
12 adform.net 1 redirects
s2.adform.net — Cisco Umbrella Rank: 6898 14yr old
c1.adform.net — Cisco Umbrella Rank: 858 13yr old
track.adform.net — Cisco Umbrella Rank: 4890 14yr old
39 KB
12 gstatic.com
fonts.gstatic.com — Cisco Umbrella Rank: 27 10yr old
www.gstatic.com — Cisco Umbrella Rank: 7 10yr old
815 KB
11 amazonaws.com
cognito-identity.eu-west-1.amazonaws.com — Cisco Umbrella Rank: 9160 12yr old
firehose.eu-west-1.amazonaws.com — Cisco Umbrella Rank: 17105 11yr old
8 KB
11 doubleclick.net 8 redirects
googleads.g.doubleclick.net — Cisco Umbrella Rank: 63 10yr old
static.doubleclick.net — Cisco Umbrella Rank: 274 10yr old
cm.g.doubleclick.net — Cisco Umbrella Rank: 330 10yr old
1002 B
9 afftrack.pro
rd.afftrack.pro 7yr old
afftrack.pro — Cisco Umbrella Rank: 915572 6yr old
11 KB
9 youtube.com
www.youtube.com — Cisco Umbrella Rank: 107 10yr old
987 KB
8 wp.pl
pixel.wp.pl — Cisco Umbrella Rank: 71101 7yr old
ssp.wp.pl — Cisco Umbrella Rank: 2864 7yr old
60 KB
7 google.com
apis.google.com — Cisco Umbrella Rank: 198 10yr old
www.google.com — Cisco Umbrella Rank: 3 14yr old
164 KB
6 gsitrix.com
p.gsitrix.com — Cisco Umbrella Rank: 105852 9yr old
o.gsitrix.com — Cisco Umbrella Rank: 118474 6yr old
59 KB
6 shoparena.pl
sklep685892.shoparena.pl 25d old
2 MB
6 googleapis.com
fonts.googleapis.com — Cisco Umbrella Rank: 42 10yr old
jnn-pa.googleapis.com — Cisco Umbrella Rank: 340 5yr old
4 KB
6 inpost.pl
inpostpay-widget-v2.inpost.pl — Cisco Umbrella Rank: 249360 2yr old
inpostpay-widget-api.inpost.pl — Cisco Umbrella Rank: 199051 2yr old
static.inpost.pl — Cisco Umbrella Rank: 214001 7yr old
76 KB
6 googletagmanager.com
www.googletagmanager.com — Cisco Umbrella Rank: 44 14yr old
995 KB
5 googlesyndication.com 2 redirects
pagead2.googlesyndication.com — Cisco Umbrella Rank: 112 10yr old
ade.googlesyndication.com — Cisco Umbrella Rank: 521 10yr old
2 KB
5 google-analytics.com
region1.google-analytics.com — Cisco Umbrella Rank: 3724 5yr old
4 adquery.io
sites.adquery.io — Cisco Umbrella Rank: 685246 6yr old
api.adquery.io — Cisco Umbrella Rank: 61777 6yr old
t1.adquery.io 5yr old
5 KB
4 mamezi.pl
cdn.appstore.mamezi.pl — Cisco Umbrella Rank: 579931 5yr old
11 KB
3 wewomedia.com
rtg.wewomedia.com — Cisco Umbrella Rank: 84978 2yr old
1 KB
3 adschoom.com
vu.adschoom.com — Cisco Umbrella Rank: 719872 14yr old
9 KB
3 altopd.com
altopd.com — Cisco Umbrella Rank: 522356 8yr old
5 KB
3 audrte.com 2 redirects
a.audrte.com — Cisco Umbrella Rank: 19405 10yr old
1 KB
3 clickonometrics.pl
delivery.clickonometrics.pl — Cisco Umbrella Rank: 104666 10yr old
sync.clickonometrics.pl — Cisco Umbrella Rank: 11838 9yr old
2 KB
3 casalemedia.com 1 redirects
dsum-sec.casalemedia.com — Cisco Umbrella Rank: 807 12yr old
2 KB
3 queisser.com
analytics.queisser.com 4yr old
25 KB
2 rtmark.net
my.rtmark.net — Cisco Umbrella Rank: 5517 10yr old
1 KB
2 loopwidget.com
loopwidget.com — Cisco Umbrella Rank: 474412 2yr old
3 KB
2 mediaconvertly.com
mediaconvertly.com — Cisco Umbrella Rank: 134269 1yr old
2 KB
2 logico3c.com
cdn.logico3c.com — Cisco Umbrella Rank: 594436 4yr old
5 KB
2 preciso.net
cdn.preciso.net — Cisco Umbrella Rank: 50338 6yr old
4 KB
2 retargeted.co
s.retargeted.co — Cisco Umbrella Rank: 116371 7yr old
33 KB
2 ciblelink.com
sv.ciblelink.com — Cisco Umbrella Rank: 369170 13yr old
2 KB
2 onaudience.com
pixel.onaudience.com — Cisco Umbrella Rank: 2383 10yr old
198 B
2 weborama.fr 2 redirects
redirect.frontend.weborama.fr — Cisco Umbrella Rank: 13754 9yr old
1 KB
2 w55c.net 2 redirects
pm.w55c.net — Cisco Umbrella Rank: 2140 12yr old
734 B
2 demdex.net 2 redirects
dpm.demdex.net — Cisco Umbrella Rank: 364 10yr old
1 KB
2 adsrvr.org
match.adsrvr.org — Cisco Umbrella Rank: 461 10yr old
297 B
2 rlcdn.com 2 redirects
idsync.rlcdn.com — Cisco Umbrella Rank: 753 10yr old
756 B
2 semasio.net 1 redirects
uipglob.semasio.net — Cisco Umbrella Rank: 1404 9yr old
1 KB
2 tangooserver.com
ban.tangooserver.com Failed — Cisco Umbrella Rank: 31680 2yr old
1 KB
2 smct.io
js.smct.io — Cisco Umbrella Rank: 43073 7yr old
48 KB
2 nunami.ai
t.nunami.ai — Cisco Umbrella Rank: 267444 2yr old
p.nunami.ai — Cisco Umbrella Rank: 628401 1yr old
8 KB
2 veoxa.com
profiling.veoxa.com — Cisco Umbrella Rank: 356688 14yr old
3 KB
2 pubmatic.com
image2.pubmatic.com — Cisco Umbrella Rank: 1018 10yr old
simage2.pubmatic.com — Cisco Umbrella Rank: 1084 10yr old
327 B
2 smartadserver.com
rtb-csync.smartadserver.com — Cisco Umbrella Rank: 850 10yr old
713 B
2 maxserver.pl
mxapp4.maxserver.pl — Cisco Umbrella Rank: 634932 6yr old
hotinfo.maxserver.pl Failed 9yr old
744 KB
1 octaadsmedia.com
octaadsmedia.com 5yr old
402 B
1 2trk.info
ban.2trk.info — Cisco Umbrella Rank: 45602 3yr old
1 KB
1 trk42.net
ai.trk42.net — Cisco Umbrella Rank: 306846 7yr old
138 B
1 audiencerun.com
d.audiencerun.com — Cisco Umbrella Rank: 572385 7yr old
845 B
1 emailpartners.net
mrtg.emailpartners.net — Cisco Umbrella Rank: 304671 8yr old
597 B
1 trackier.com
static-cdn.trackier.com — Cisco Umbrella Rank: 39964 4yr old
953 B
1 bsmartdata.com
pixel.bsmartdata.com — Cisco Umbrella Rank: 318406 9yr old
369 B
1 facemyads.co
tag.facemyads.co 4yr old
32 KB
1 retagtraffic.com
trk.retagtraffic.com 2yr old
1 KB
1 cookieless-data.com
js.cookieless-data.com — Cisco Umbrella Rank: 179575 6yr old
2 KB
1 apptracker.stream
apptracker.stream — Cisco Umbrella Rank: 802407 9yr old
620 B
1 bbd-tag.de 1 redirects
bbd-tag.de — Cisco Umbrella Rank: 773215 9yr old
126 B
1 onetag-sys.com
onetag-sys.com — Cisco Umbrella Rank: 846 11yr old
183 B
1 3lift.com
eb2.3lift.com — Cisco Umbrella Rank: 593 10yr old
140 B
1 mediarithmics.com
cookie-matching.mediarithmics.com — Cisco Umbrella Rank: 3573 10yr old
180 B
1 smaato.net
s.ad.smaato.net — Cisco Umbrella Rank: 944 6yr old
66 B
1 teads.tv
sync.teads.tv — Cisco Umbrella Rank: 1289 10yr old
276 B
1 id5-sync.com
id5-sync.com — Cisco Umbrella Rank: 600 9yr old
1 KB
1 adition.com
dsp.adfarm1.adition.com — Cisco Umbrella Rank: 8191 10yr old
235 B
1 agkn.com
aa.agkn.com — Cisco Umbrella Rank: 761 10yr old
307 B
1 userreport.com
pdw-adf.userreport.com — Cisco Umbrella Rank: 17606 8yr old
445 B
1 adsafety.net
cm.adsafety.net — Cisco Umbrella Rank: 45529 9yr old
229 B
1 openx.net
eu-u.openx.net — Cisco Umbrella Rank: 1810 10yr old
278 B
1 crwdcntrl.net
sync.crwdcntrl.net — Cisco Umbrella Rank: 972 9yr old
268 B
1 exelator.com
loadm.exelator.com — Cisco Umbrella Rank: 3046 13yr old
325 B
1 eyeota.net
ps.eyeota.net — Cisco Umbrella Rank: 1260 13yr old
354 B
1 bidswitch.net
x.bidswitch.net — Cisco Umbrella Rank: 561 13yr old
164 B
1 fwmrm.net
user-sync.fwmrm.net — Cisco Umbrella Rank: 941 1yr old
504 B
1 adscale.de
ih.adscale.de — Cisco Umbrella Rank: 2945 11yr old
59 B
1 rubiconproject.com
token.rubiconproject.com — Cisco Umbrella Rank: 731 10yr old
214 B
1 yieldlab.net
ad.yieldlab.net — Cisco Umbrella Rank: 4609 10yr old
235 B
1 360yield.com
ad.360yield.com — Cisco Umbrella Rank: 895 14yr old
199 B
1 seadform.net
server.seadform.net — Cisco Umbrella Rank: 28504 9yr old
676 B
1 roeye.com
lantern.roeye.com — Cisco Umbrella Rank: 9053 10yr old
181 B
1 roeyecdn.com
lantern.roeyecdn.com — Cisco Umbrella Rank: 8534 8yr old
2 KB
1 mainadv.com
www.mainadv.com — Cisco Umbrella Rank: 46866 14yr old
963 B
1 upsellit.com
www.upsellit.com — Cisco Umbrella Rank: 12183 10yr old
12 KB
1 goadservices.com
ssp.goadservices.com — Cisco Umbrella Rank: 38805 3yr old
528 B
1 smct.co
smct.co — Cisco Umbrella Rank: 29392 11yr old
6 KB
1 dwin1.com
www.dwin1.com — Cisco Umbrella Rank: 5832 14yr old
18 KB
1 ytimg.com
i.ytimg.com — Cisco Umbrella Rank: 123 10yr old
166 KB
1 wpcdn.pl
std.wpcdn.pl — Cisco Umbrella Rank: 30664 9yr old
32 KB
1 maxsote.pl
pprzesylka.maxsote.pl 3yr old
17 KB
1 ceneo.pl
ssl.ceneo.pl — Cisco Umbrella Rank: 128358 10yr old
3 KB
1 cloudflare.com
cdnjs.cloudflare.com — Cisco Umbrella Rank: 277 13yr old
3 KB
1 dcsaascdn.net
dcsaascdn.net — Cisco Umbrella Rank: 222159 6yr old
3 KB
0 owltrack.com Failed
rev.owltrack.com Failed 7yr old
0 fulllab.com.br Failed
tags.fulllab.com.br Failed 9yr old
0 contentexchange.me Failed
match.contentexchange.me Failed 7yr old
0 adnxs.com Failed
secure.adnxs.com Failed 10yr old
335 98
Domain Requested by
69 sklep.doppelherz.pl sklep.doppelherz.pl
dcsaascdn.net
19 trustmate.io sklep.doppelherz.pl
trustmate.io
10 c1.adform.net 1 redirects sklep.doppelherz.pl
track.adform.net
c1.adform.net
9 fonts.gstatic.com www.youtube.com
fonts.googleapis.com
www.google.com
sklep.doppelherz.pl
9 www.youtube.com sklep.doppelherz.pl
www.youtube.com
8 afftrack.pro rd.afftrack.pro
afftrack.pro
8 cm.g.doubleclick.net 7 redirects sklep.doppelherz.pl
7 firehose.eu-west-1.amazonaws.com js.smct.io
7 cdn.doofinder.com eu1-config.doofinder.com
cdn.doofinder.com
6 sklep685892.shoparena.pl sklep.doppelherz.pl
6 pixel.wp.pl sklep.doppelherz.pl
pixel.wp.pl
6 www.googletagmanager.com sklep.doppelherz.pl
www.googletagmanager.com
5 p.gsitrix.com p.gsitrix.com
5 region1.google-analytics.com www.googletagmanager.com
4 cognito-identity.eu-west-1.amazonaws.com js.smct.io
4 ade.googlesyndication.com 2 redirects sklep.doppelherz.pl
4 fonts.googleapis.com www.google.com
4 cdn.appstore.mamezi.pl sklep.doppelherz.pl
4 apis.google.com sklep.doppelherz.pl
apis.google.com
www.gstatic.com
3 rtg.wewomedia.com sklep.doppelherz.pl
rtg.wewomedia.com
3 vu.adschoom.com sklep.doppelherz.pl
vu.adschoom.com
3 altopd.com dfd.doppelherz.pl
altopd.com
3 a.audrte.com 2 redirects c1.adform.net
3 dsum-sec.casalemedia.com 1 redirects sklep.doppelherz.pl
c1.adform.net
3 inpostpay-widget-api.inpost.pl inpostpay-widget-v2.inpost.pl
3 analytics.queisser.com sklep.doppelherz.pl
analytics.queisser.com
3 www.gstatic.com www.google.com
www.gstatic.com
3 www.google.com www.youtube.com
apis.google.com
www.gstatic.com
3 dfd.doppelherz.pl sklep.doppelherz.pl
dfd.doppelherz.pl
2 my.rtmark.net static-cdn.trackier.com
2 loopwidget.com sklep.doppelherz.pl
loopwidget.com
2 mediaconvertly.com sklep.doppelherz.pl
mediaconvertly.com
2 cdn.logico3c.com sklep.doppelherz.pl
cdn.logico3c.com
2 cdn.preciso.net sklep.doppelherz.pl
cdn.preciso.net
2 s.retargeted.co sklep.doppelherz.pl
s.retargeted.co
2 sv.ciblelink.com profiling.veoxa.com
sv.ciblelink.com
2 pixel.onaudience.com c1.adform.net
2 redirect.frontend.weborama.fr 2 redirects
2 pm.w55c.net 2 redirects
2 dpm.demdex.net 2 redirects
2 match.adsrvr.org c1.adform.net
2 idsync.rlcdn.com 2 redirects
2 uipglob.semasio.net 1 redirects c1.adform.net
2 eu1-api.doofinder.com cdn.doofinder.com
2 ban.tangooserver.com www.mainadv.com
cdn.logico3c.com
2 js.smct.io smct.co
2 delivery.clickonometrics.pl www.dwin1.com
2 profiling.veoxa.com www.dwin1.com
profiling.veoxa.com
2 eu1-recommendations.doofinder.com cdn.doofinder.com
2 t1.adquery.io sklep.doppelherz.pl
2 static.inpost.pl sklep.doppelherz.pl
2 eu1-search.doofinder.com cdn.doofinder.com
2 rtb-csync.smartadserver.com sklep.doppelherz.pl
c1.adform.net
2 jnn-pa.googleapis.com www.youtube.com
2 ssp.wp.pl pixel.wp.pl
std.wpcdn.pl
2 googleads.g.doubleclick.net 1 redirects www.youtube.com
2 mxapp4.maxserver.pl sklep.doppelherz.pl
1 octaadsmedia.com sklep.doppelherz.pl
1 ban.2trk.info cdn.preciso.net
1 o.gsitrix.com p.gsitrix.com
1 ai.trk42.net sklep.doppelherz.pl
1 d.audiencerun.com
1 mrtg.emailpartners.net
1 static-cdn.trackier.com sklep.doppelherz.pl
1 pixel.bsmartdata.com dfd.doppelherz.pl
1 tag.facemyads.co sklep.doppelherz.pl
1 trk.retagtraffic.com dfd.doppelherz.pl
1 js.cookieless-data.com sklep.doppelherz.pl
1 apptracker.stream
1 bbd-tag.de 1 redirects
1 rd.afftrack.pro sklep.doppelherz.pl
1 onetag-sys.com c1.adform.net
1 eb2.3lift.com c1.adform.net
1 cookie-matching.mediarithmics.com c1.adform.net
1 s.ad.smaato.net c1.adform.net
1 sync.teads.tv c1.adform.net
1 id5-sync.com c1.adform.net
1 dsp.adfarm1.adition.com c1.adform.net
1 aa.agkn.com c1.adform.net
1 pdw-adf.userreport.com c1.adform.net
1 simage2.pubmatic.com c1.adform.net
1 cm.adsafety.net c1.adform.net
1 eu-u.openx.net c1.adform.net
1 sync.crwdcntrl.net c1.adform.net
1 loadm.exelator.com c1.adform.net
1 ps.eyeota.net c1.adform.net
1 x.bidswitch.net c1.adform.net
1 user-sync.fwmrm.net c1.adform.net
1 ih.adscale.de c1.adform.net
1 token.rubiconproject.com c1.adform.net
1 ad.yieldlab.net c1.adform.net
1 ad.360yield.com c1.adform.net
1 server.seadform.net sklep.doppelherz.pl
1 sync.clickonometrics.pl delivery.clickonometrics.pl
1 lantern.roeye.com sklep.doppelherz.pl
1 p.nunami.ai t.nunami.ai
1 track.adform.net s2.adform.net
1 lantern.roeyecdn.com www.dwin1.com
1 t.nunami.ai www.dwin1.com
1 www.mainadv.com www.dwin1.com
1 www.upsellit.com www.dwin1.com
1 tagmanager.sklep.doppelherz.pl www.googletagmanager.com
1 api.adquery.io sites.adquery.io
1 image2.pubmatic.com sklep.doppelherz.pl
1 ssp.goadservices.com std.wpcdn.pl
1 pagead2.googlesyndication.com www.googletagmanager.com
1 sites.adquery.io sklep.doppelherz.pl
1 s2.adform.net sklep.doppelherz.pl
1 smct.co www.googletagmanager.com
1 www.dwin1.com www.googletagmanager.com
1 i.ytimg.com www.youtube.com
1 std.wpcdn.pl ssp.wp.pl
1 static.doubleclick.net www.youtube.com
1 inpostpay-widget-v2.inpost.pl sklep.doppelherz.pl
1 pprzesylka.maxsote.pl sklep.doppelherz.pl
1 ssl.ceneo.pl sklep.doppelherz.pl
1 papi.trustmate.io sklep.doppelherz.pl
1 cdnjs.cloudflare.com sklep.doppelherz.pl
1 eu1-config.doofinder.com sklep.doppelherz.pl
1 dcsaascdn.net sklep.doppelherz.pl
0 rev.owltrack.com Failed sklep.doppelherz.pl
0 tags.fulllab.com.br Failed sklep.doppelherz.pl
0 match.contentexchange.me Failed c1.adform.net
0 secure.adnxs.com Failed c1.adform.net
0 hotinfo.maxserver.pl Failed sklep.doppelherz.pl
335 125
Subject Issuer Validity Valid
www.sklep.doppelherz.pl
Shoper DV TLS G2 R34 CA
2026-05-18 -
2026-12-03
7mo crt.sh
dcsaascdn.net
WE1
2026-09-01 -
2026-11-30
3mo crt.sh
dfd.doppelherz.pl
YE2
2026-08-28 -
2026-11-26
3mo crt.sh
doofinder.com
Amazon RSA 2048 M01
2026-07-09 -
2027-01-22
7mo crt.sh
trustmate.io
Amazon RSA 2048 M01
2025-11-24 -
2026-12-23
1yr crt.sh
cdnjs.cloudflare.com
WE1
2026-09-07 -
2026-12-06
3mo crt.sh
*.apis.google.com
WE2
2026-09-04 -
2026-11-27
3mo crt.sh
cdn.appstore.mamezi.pl
Amazon RSA 2048 M04
2025-10-26 -
2026-11-24
1yr crt.sh
shoper.trustmate.io
YR2
2026-08-28 -
2026-11-26
3mo crt.sh
*.google-analytics.com
WE2
2026-09-04 -
2026-11-27
3mo crt.sh
*.ceneo.pl
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2026-04-16 -
2026-10-31
7mo crt.sh
*.wp.pl
RapidSSL TLS RSA CA G1
2026-09-11 -
2027-03-17
6mo crt.sh
*.google.com
WE2
2026-08-10 -
2026-11-02
3mo crt.sh
*.maxsote.pl
Sectigo Public Server Authentication CA DV R36
2026-03-11 -
2027-04-10
1yr crt.sh
mail.mxapp4.maxserver.pl
YR2
2026-07-21 -
2026-10-19
3mo crt.sh
inpost.pl
WE1
2026-08-11 -
2026-11-09
3mo crt.sh
1648062886.rsc.cdn77.org
YE2
2026-08-01 -
2026-10-30
3mo crt.sh
upload.video.google.com
WE2
2026-09-04 -
2026-11-27
3mo crt.sh
*.gstatic.com
WE2
2026-09-04 -
2026-11-27
3mo crt.sh
*.doubleclick.net
WE2
2026-09-04 -
2026-11-27
3mo crt.sh
*.wpcdn.pl
RapidSSL TLS RSA CA G1
2026-05-12 -
2026-11-26
7mo crt.sh
edgestatic.com
WR2
2026-09-04 -
2026-11-27
3mo crt.sh
*.dwin1.com
Amazon RSA 2048 M01
2026-08-31 -
2027-03-16
7mo crt.sh
smct.co
Amazon RSA 2048 M04
2025-12-17 -
2027-01-14
1yr crt.sh
track.adform.net
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2026-08-28 -
2026-10-06
1mo crt.sh
analytics.queisser.com
YR2
2026-09-03 -
2026-12-02
3mo crt.sh
adquery.io
WE1
2026-08-27 -
2026-11-25
3mo crt.sh
*.g.doubleclick.net
WE2
2026-09-04 -
2026-11-27
3mo crt.sh
*.goadservices.com
RapidSSL TLS ECC CA G1
2025-11-06 -
2026-11-05
1yr crt.sh
*.smartadserver.com
DigiCert Global G3 TLS ECC SHA384 2020 CA1
2026-02-04 -
2027-02-10
1yr crt.sh
*.pubmatic.com
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2026-02-18 -
2027-03-19
1yr crt.sh
*.inpost.pl
RapidSSL TLS RSA CA G1
2025-11-14 -
2026-12-15
1yr crt.sh
t1.adquery.io
YR2
2026-08-09 -
2026-11-07
3mo crt.sh
tagmanager.sklep.doppelherz.pl
YR1
2026-07-22 -
2026-10-20
3mo crt.sh
*.upsellit.com
YE2
2026-07-22 -
2026-10-20
3mo crt.sh
mainadv.com
WE1
2026-09-02 -
2026-12-01
3mo crt.sh
profiling.veoxa.com
YR1
2026-08-19 -
2026-11-17
3mo crt.sh
*.clickonometrics.pl
Certum DV TLS G2 R39 CA
2026-02-11 -
2027-02-11
1yr crt.sh
t.nunami.ai
YE1
2026-08-25 -
2026-11-23
3mo crt.sh
*.roeyecdn.com
Amazon RSA 2048 M04
2026-06-29 -
2027-01-12
7mo crt.sh
smct.io
WE1
2026-08-14 -
2026-11-12
3mo crt.sh
tangooserver.com
WE1
2026-07-22 -
2026-10-20
3mo crt.sh
cognito-identity.eu-west-1.amazonaws.com
Amazon RSA 2048 M04
2025-12-25 -
2027-01-23
1yr crt.sh
p.nunami.ai
YE1
2026-08-20 -
2026-11-18
3mo crt.sh
*.roeye.com
Amazon RSA 2048 M04
2026-08-28 -
2027-03-13
7mo crt.sh
*.seadform.net
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2026-08-11 -
2026-11-12
3mo crt.sh
*.shoparena.pl
Shoper DV TLS G2 R34 CA
2026-02-25 -
2027-02-25
1yr crt.sh
*.360yield.com
Amazon RSA 2048 M04
2026-07-15 -
2027-01-28
7mo crt.sh
*.yieldlab.net
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2026-06-10 -
2026-12-25
7mo crt.sh
*.rubiconproject.com
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2026-08-31 -
2027-03-17
7mo crt.sh
*.adscale.de
Amazon RSA 2048 M04
2026-04-19 -
2026-11-02
7mo crt.sh
*.fwmrm.net
Sectigo Public Server Authentication CA OV R36
2026-08-18 -
2027-03-04
7mo crt.sh
*.bidswitch.net
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2026-07-08 -
2026-10-10
3mo crt.sh
casalemedia.com
YE2
2026-07-24 -
2026-10-22
3mo crt.sh
eyeota.net
GoGetSSL RSA DV CA
2026-04-21 -
2026-11-05
7mo crt.sh
*.exelator.com
GlobalSign RSA OV SSL CA 2018
2026-07-02 -
2027-01-17
7mo crt.sh
*.crwdcntrl.net
Amazon RSA 2048 M01
2026-07-11 -
2027-01-24
7mo crt.sh
*.openx.net
RapidSSL TLS RSA CA G1
2026-07-18 -
2027-02-01
7mo crt.sh
*.adsafety.net
YE1
2026-09-06 -
2026-12-05
3mo crt.sh
*.userreport.com
Amazon RSA 2048 M01
2026-08-18 -
2027-03-03
7mo crt.sh
agkn.com
GeoTrust TLS RSA CA G1
2026-09-09 -
2027-03-26
7mo crt.sh
*.adfarm1.adition.com
Certum DV TLS G2 R39 CA
2026-05-04 -
2026-11-19
7mo crt.sh
*.adsrvr.org
GlobalSign GCC R3 DV TLS CA 2020
2026-03-04 -
2027-04-02
1yr crt.sh
id5-sync.com
YE1
2026-09-01 -
2026-11-30
3mo crt.sh
*.teads.tv
Thawte TLS RSA CA G1
2026-03-29 -
2026-10-13
7mo crt.sh
*.ad.smaato.net
WR1
2026-08-14 -
2026-11-12
3mo crt.sh
*.mediarithmics.com
GandiCert
2026-02-09 -
2027-02-23
1yr crt.sh
*.onaudience.com
Go Daddy Secure Certificate Authority - G2
2026-03-30 -
2026-10-14
7mo crt.sh
*.3lift.com
Amazon RSA 2048 M04
2026-01-12 -
2027-02-09
1yr crt.sh
*.onetag-sys.com
DigiCert Global G3 TLS ECC SHA384 2020 CA1
2025-12-23 -
2027-01-22
1yr crt.sh
sv.ciblelink.com
YE2
2026-07-26 -
2026-10-24
3mo crt.sh
firehose.eu-west-1.amazonaws.com
Amazon RSA 2048 M01
2026-06-10 -
2026-12-24
7mo crt.sh
afftrack.pro
WE1
2026-08-31 -
2026-11-29
3mo crt.sh
retargeted.co
WE1
2026-09-02 -
2026-12-01
3mo crt.sh
*.cookieless-data.com
RapidSSL TLS RSA CA G1
2026-03-10 -
2026-09-24
7mo crt.sh
altopd.com
YR2
2026-09-06 -
2026-12-05
3mo crt.sh
preciso.net
WE1
2026-08-02 -
2026-10-31
3mo crt.sh
logico3c.com
WE1
2026-07-30 -
2026-10-28
3mo crt.sh
retagtraffic.com
WE1
2026-07-31 -
2026-10-30
3mo crt.sh
facemyads.co
WE1
2026-09-03 -
2026-12-02
3mo crt.sh
vu.adschoom.com
YE2
2026-07-26 -
2026-10-24
3mo crt.sh
pixel.bsmartdata.com
YR2
2026-07-24 -
2026-10-22
3mo crt.sh
wewomedia.com
WR3
2026-09-07 -
2026-12-06
3mo crt.sh
mediaconvertly.com
WE1
2026-07-29 -
2026-10-27
3mo crt.sh
*.trackier.com
YR2
2026-08-14 -
2026-11-12
3mo crt.sh
*.emailpartners.net
cyber_Folks
2026-03-16 -
2026-10-01
7mo crt.sh
*.audiencerun.com
Amazon RSA 2048 M04
2026-07-11 -
2027-01-24
7mo crt.sh
ai.trk42.net
WR3
2026-09-02 -
2026-12-01
3mo crt.sh
p.gsitrix.com
YE2
2026-09-02 -
2026-12-01
3mo crt.sh
loopwidget.com
WE1
2026-09-08 -
2026-12-07
3mo crt.sh
o.gsitrix.com
YR2
2026-08-31 -
2026-11-29
3mo crt.sh
2trk.info
WE1
2026-08-01 -
2026-10-31
3mo crt.sh
octaadsmedia.com
YE2
2026-08-09 -
2026-11-07
3mo crt.sh
my.rtmark.net
WE1
2026-08-18 -
2026-11-16
3mo crt.sh

This page contains 12 frames:

Primary Page: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Frame ID: EEEE06935CEBAD07E7B4CE78E35A401F
Requests: 251 HTTP requests in this frame

Frame: https://www.youtube.com/embed/RIenpVjeLR8?si=BHrZAFVtmPsydAwu
Frame ID: 90C8210D9080992DD7CFB52CD02BE533
Requests: 15 HTTP requests in this frame

Frame: https://ssp.wp.pl/ecom/usersync.html?consent=1&partner_id=WP-ADS-WP-ADS-LN9ZN-JUK
Frame ID: ED5446050B9C0281367671E1261CB53E
Requests: 10 HTTP requests in this frame

Frame: https://www.google.com/shopping/merchantverse/?usegapi=1&merchant_id=569730759&position=BOTTOM_RIGHT&hl=pl&origin=https%3A%2F%2Fsklep.doppelherz.pl&gsrc=3p&jsh=m%3B%2F_%2Fscs%2Fabc-static%2F_%2Fjs%2Fk%3Dgapi.lb.pl.r2bYKzcHidM.O%2Fd%3D1%2Frs%3DAHpOoo_W5oST4w0nWzAS8ntjYKme90h9Wg%2Fm%3D__features__
Frame ID: 0227F9FAB9AAD0BF5DF3BA6A849A5236
Requests: 11 HTTP requests in this frame

Frame: https://api.adquery.io/storage
Frame ID: B5CE1DFD858CABEA8E0496D47A6DF9C7
Requests: 1 HTTP requests in this frame

Frame: https://www.mainadv.com/retargeting/live/zanox_rtg.aspx?Key=ZX&visitorIp=DOPPELHERZ_AWI_PL&pageType=product
Frame ID: F1293540D21058FE41154DF643814097
Requests: 2 HTTP requests in this frame

Frame: https://ban.tangooserver.com/rtb/google/cookiematch.aspx?id=tangoomedia&cok15=awi_dpp_pl&cnty15=POL&Referrer=https%3A%2F%2Fsklep.doppelherz.pl%2F&ty_orderid=&ty_orderamt=0&pdt_id=&pdt_category_list=&token=DOPPELHERZ_AWI_PL&pagetype=product&t=4&ProgramName=DOPPELHERZ_AWI_PL&AudienceId=9898&CampaignId=66742&gdpr=0&BrowserCheck=True&google_gid=CAESEEiSW-Fd8L3g4FnCSbvue8c&google_cver=1&google_ula=7241462486,0
Frame ID: E82A40FDA879E03535CC4B2CF55C2304
Requests: 1 HTTP requests in this frame

Frame: https://sync.clickonometrics.pl/adexchange/set-cookie?id=&advid=&google_gid=CAESEMMi5pC-_P0duSsCwSLeI4c&google_cver=1
Frame ID: AA994DEB4BA6A58112442778C9740284
Requests: 1 HTTP requests in this frame

Frame: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Frame ID: 25427090B800C7D886515484C3E357AA
Requests: 39 HTTP requests in this frame

Frame: https://p.gsitrix.com/page/?a=60ef70b6a8b131626304694&p=product&prid={IDPRODUIT}&av=0&as=trafficpark&ax=1&w=doppelherz.pl&gdpr={GDPR}&gdpr_consent={GDPR_CONSENT}&ref={PAGE}
Frame ID: D8C358EACC1253BEC2D591EF184ADA60
Requests: 6 HTTP requests in this frame

Frame: https://ban.tangooserver.com/rtb/google/cookiematch.aspx?id=tangoomedia&cok15=kwo_dpp_pl&cnty15=POL&t=4&ProgramName=DOPPELHERZ_PL8879&AudienceId=8879&CampaignId=65997&Referrer=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&ProductId=412&ProductCategoryList=Doppelherz%20system&PageType=product&Browsercheck=true&gdpr=0&a15=false&dw15=false&ls15=false&google_gid=CAESEEiSW-Fd8L3g4FnCSbvue8c&google_cver=1&google_ula=7241462486,0
Frame ID: 336DB07AD0FC0FF3D2A921B19FBC6824
Requests: 1 HTTP requests in this frame

Frame: https://ban.2trk.info/rtb/p0n/us6mch?id=p_srl&cok15=pne_dpp_pl&cnty15=POL&t=4&ProgramName=DOPPELHERZ_PL&AudienceId=3987&CampaignId=63729&Referrer=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&ProductId=412&ProductCategoryList=Doppelherz%20system&PageType=product&Browsercheck=true&gdpr=0&gdpr_pd=0&a15=false&dw15=false&google_gid=CAESEPrRQqX8UJgcOMF4Kmq2HUw&google_cver=1&google_ula=6490516189,0
Frame ID: 04533532A532FEC35BB5E1A5C224A4F0
Requests: 1 HTTP requests in this frame

Screenshot Go Pro

Only in urlscan Pro

Use the Visual Search feature to find pages with visually similar screenshots.
Click for more information
Free trials of urlscan Pro are available.

Page Title

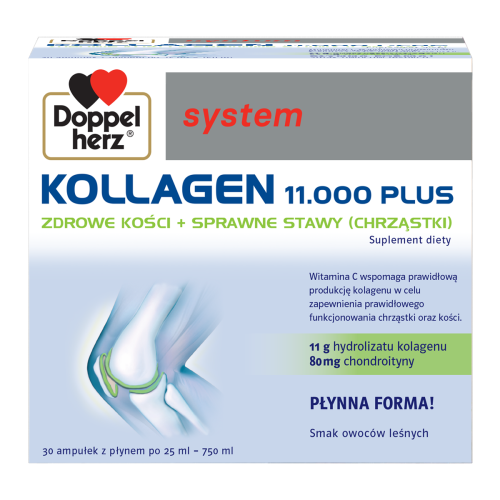
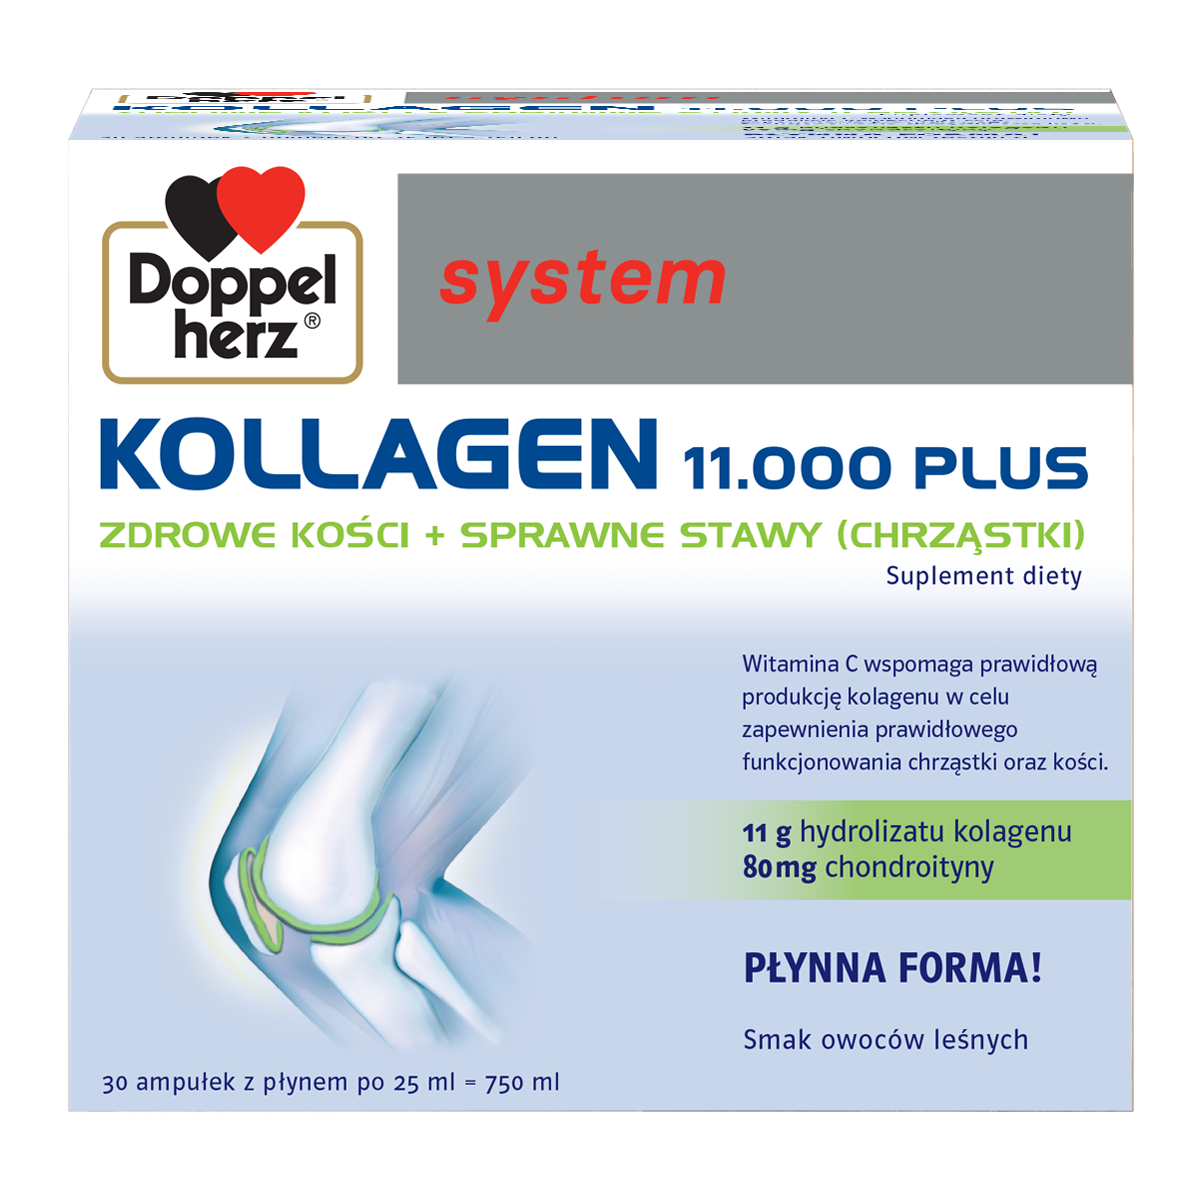
Doppelherz system Kollagen 11.000 PLUS | 30 ampułek - sklep Doppelherz

Detected technologies

(Issue trackers)
Overall confidence: 100%
Detected patterns
  • \.userreport\.com/

(Search engines)
Overall confidence: 100%
Detected patterns
  • cdn\.doofinder\.com/

(Video players)
Overall confidence: 100%
Detected patterns
  • \.youtube\.com/

(JavaScript frameworks)
Overall confidence: 100%
Detected patterns
  • mustache(?:\.min)?\.js

(Analytics)
Overall confidence: 50%
Detected patterns
  • sp\.js

(Advertising)
Overall confidence: 100%
Detected patterns
  • \.adform\.net/

(Segmentation)
Overall confidence: 100%
Detected patterns

(Affiliate programs)
Overall confidence: 100%
Detected patterns
  • dwin1\.com

(CDN)
Overall confidence: 100%
Detected patterns
  • cdnjs\.cloudflare\.com

(JavaScript libraries)
Overall confidence: 100%
Detected patterns
  • /ClientJS/(?:(\d.*?)/)?

(Security)
Overall confidence: 100%
Detected patterns

(Advertising)
Overall confidence: 100%
Detected patterns
  • \.doubleclick\.net

(Font scripts)
Overall confidence: 100%
Detected patterns
  • (?:F|f)o(?:n|r)t-?(?:A|a)wesome(?:.*?([0-9a-fA-F]{7,40}|[\d]+(?:.[\d]+(?:.[\d]+)?)?)|)

(Advertising)
Overall confidence: 100%
Detected patterns
  • fwmrm\.net

(Advertising)
Overall confidence: 100%
Detected patterns
  • googlesyndication\.com/

(Analytics)
Overall confidence: 100%
Detected patterns
  • googletagmanager\.com/gtag/js

(Tag managers)
Overall confidence: 100%
Detected patterns
  • googletagmanager\.com/gtm\.js
  • \.googletagmanager\.com/

(Advertising)
Overall confidence: 100%
Detected patterns
  • ^https://(?:cdn\.)?id5-sync\.com/

(Advertising)
Overall confidence: 100%
Detected patterns
  • \.mainadv\.com/

(Advertising)
Overall confidence: 100%
Detected patterns
  • https?://[^/]*\.openx\.net

(Advertising)
Overall confidence: 100%
Detected patterns
  • https?://[^/]*\.pubmatic\.com

(Advertising)
Overall confidence: 100%
Detected patterns
  • https?://[^/]*\.rubiconproject\.com

(Retargeting)
Overall confidence: 100%
Detected patterns
  • \.?smct\.(?:io|co)/

(Advertising)
Overall confidence: 100%
Detected patterns
  • teads\.tv

(Advertising)
Overall confidence: 100%
Detected patterns
  • \.adsrvr\.org/

(Cart abandonment)
Overall confidence: 100%
Detected patterns
  • www\.upsellit\.com/

(Advertising)
Overall confidence: 100%
Detected patterns
  • ^https?://(?:[^/]+\.)?yieldlab\.net/

Page Statistics

335
Requests

91 %
HTTPS

0 %
IPv6

98
Domains

125
Subdomains

109
IPs

13
Countries

9283 kB
Transfer

19358 kB
Size

74
Cookies

Redirected requests

There were HTTP redirect chains for the following requests:

Request Chain 138
  • https://googleads.g.doubleclick.net/pagead/id HTTP 302
  • https://googleads.g.doubleclick.net/pagead/id?slf_rd=1
Request Chain 177
  • https://cm.g.doubleclick.net/pixel?google_nid=gopl_sp_z_oo&process_consent=T&google_ula=9190014480&google_hm=Z28tMDFNMk1GRFFHQjQ5SEtUUVA3NzFQVzhXM0c= HTTP 302
  • https://cm.g.doubleclick.net/pixel?google_nid=gopl_sp_z_oo&process_consent=T&google_ula=9190014480&google_hm=Z28tMDFNMk1GRFFHQjQ5SEtUUVA3NzFQVzhXM0c=&google_tc=
Request Chain 178
  • https://c1.adform.net/serving/cookie/match?party=10013&gdpr=0&cid=53df3e2c6c9971933f0b8c6acf715e73:3ac0da:1789541144:v3 HTTP 302
  • https://c1.adform.net/serving/cookie/match?CC=1&party=10013&gdpr=0&cid=53df3e2c6c9971933f0b8c6acf715e73:3ac0da:1789541144:v3
Request Chain 179
  • https://dsum-sec.casalemedia.com/rum?cm_dsp_id=264&gdpr=0&external_user_id=go-01M2MFDQGB49HKTQP771PW8W3G HTTP 302
  • https://dsum-sec.casalemedia.com/rum?cm_dsp_id=264&gdpr=0&external_user_id=go-01M2MFDQGB49HKTQP771PW8W3G&C=1
Request Chain 219
  • https://ade.googlesyndication.com/ddm/activity/src=12904208;type=02;cat=0223_000;rcb=12;ord=6477499443053;npa=1;u6=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus;uaa=x86;uab=64;uafvl=Chromium%3B153.0.8010.36%7CGoogle%2520Chrome%3B153.0.8010.36%7CNot_A%2520Brand%3B8.0.0.0;uamb=0;uam=;uap=Linux;uapv=;uaw=0;pscdl=denied;frm=0;user_data_mode=a;_tu=KFA;gtm=45fe69e1v9190271573z8865320812za20gzb865320812zd865320812xea;gcs=G100;gcd=13q3q3q2q5l1;dma_cps=-;dma=1;dc_fmt=8;tag_exp=115938465~115938468~118897920~118897930~119791748~120213116~120385422~120469145~120469153;epver=2;~oref=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus HTTP 302
  • https://ade.googlesyndication.com/ddm/activity/src=12904208;dc_pre=COH5_aLA8pYDFakpZgkdgWMpPw;type=02;cat=0223_000;rcb=12;ord=6477499443053;npa=1;u6=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus;uaa=x86;uab=64;uafvl=Chromium%3B153.0.8010.36%7CGoogle%2520Chrome%3B153.0.8010.36%7CNot_A%2520Brand%3B8.0.0.0;uamb=0;uam=;uap=Linux;uapv=;uaw=0;pscdl=denied;frm=0;user_data_mode=a;_tu=KFA;gtm=45fe69e1v9190271573z8865320812za20gzb865320812zd865320812xea;gcs=G100;gcd=13q3q3q2q5l1;dma_cps=-;dma=1;dc_fmt=8;tag_exp=115938465~115938468~118897920~118897930~119791748~120213116~120385422~120469145~120469153;epver=2;~oref=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus
Request Chain 220
  • https://ade.googlesyndication.com/ddm/activity/src=12904208;type=02;cat=0223_0;rcb=12;ord=6431953893739;npa=1;u3=Doppelherz%C2%AE%20system%20KOLLAGEN%2011.000%20PLUS%2C%2030%20ampu%C5%82ek%20po%2025ml;u4=122.7;u6=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus;u7=412;uaa=x86;uab=64;uafvl=Chromium%3B153.0.8010.36%7CGoogle%2520Chrome%3B153.0.8010.36%7CNot_A%2520Brand%3B8.0.0.0;uamb=0;uam=;uap=Linux;uapv=;uaw=0;pscdl=denied;frm=0;user_data_mode=a;_tu=KFA;gtm=45fe69e1v9190271573z8865320812za20gzb865320812zd865320812xea;gcs=G100;gcd=13q3q3q2q5l1;dma_cps=-;dma=1;dc_fmt=8;tag_exp=115938465~115938468~118897920~118897930~119791748~120213116~120385422~120469145~120469153;epver=2;~oref=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus HTTP 302
  • https://ade.googlesyndication.com/ddm/activity/src=12904208;dc_pre=CLX2_aLA8pYDFQRV5wEdJfQ8Zg;type=02;cat=0223_0;rcb=12;ord=6431953893739;npa=1;u3=Doppelherz%C2%AE%20system%20KOLLAGEN%2011.000%20PLUS%2C%2030%20ampu%C5%82ek%20po%2025ml;u4=122.7;u6=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus;u7=412;uaa=x86;uab=64;uafvl=Chromium%3B153.0.8010.36%7CGoogle%2520Chrome%3B153.0.8010.36%7CNot_A%2520Brand%3B8.0.0.0;uamb=0;uam=;uap=Linux;uapv=;uaw=0;pscdl=denied;frm=0;user_data_mode=a;_tu=KFA;gtm=45fe69e1v9190271573z8865320812za20gzb865320812zd865320812xea;gcs=G100;gcd=13q3q3q2q5l1;dma_cps=-;dma=1;dc_fmt=8;tag_exp=115938465~115938468~118897920~118897930~119791748~120213116~120385422~120469145~120469153;epver=2;~oref=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus
Request Chain 223
  • https://cm.g.doubleclick.net/pixel?google_nid=tangoomedia&google_ula=7241462486&google_cm&cok15=awi_dpp_pl&cnty15=POL&Referrer=https%3a%2f%2fsklep.doppelherz.pl%2f&ty_orderid=&ty_orderamt=0&pdt_id=&pdt_category_list=&token=DOPPELHERZ_AWI_PL&pagetype=product&t=4&ProgramName=DOPPELHERZ_AWI_PL&AudienceId=9898&CampaignId=66742&gdpr=0&BrowserCheck=True HTTP 302
  • https://ban.tangooserver.com/rtb/google/cookiematch.aspx?id=tangoomedia&cok15=awi_dpp_pl&cnty15=POL&Referrer=https%3A%2F%2Fsklep.doppelherz.pl%2F&ty_orderid=&ty_orderamt=0&pdt_id=&pdt_category_list=&token=DOPPELHERZ_AWI_PL&pagetype=product&t=4&ProgramName=DOPPELHERZ_AWI_PL&AudienceId=9898&CampaignId=66742&gdpr=0&BrowserCheck=True&google_gid=CAESEEiSW-Fd8L3g4FnCSbvue8c&google_cver=1&google_ula=7241462486,0
Request Chain 231
  • https://cm.g.doubleclick.net/pixel?google_nid=360ecom_sp_z_oo_2&google_hm=NTM4MjEwXzM3MzAyMQ&google_cm&process_consent=T&advid= HTTP 302
  • https://sync.clickonometrics.pl/adexchange/set-cookie?id=&advid=&google_gid=CAESEMMi5pC-_P0duSsCwSLeI4c&google_cver=1
Request Chain 250
  • https://uipglob.semasio.net/adform/1/info?sType=sync&sExtCookieId=5351721985196806187&sInitiator=external HTTP 302
  • https://uipglob.semasio.net/adform/1/info2?sType=sync&sExtCookieId=5351721985196806187&sInitiator=external
Request Chain 253
  • https://idsync.rlcdn.com/398366.gif?partner_uid=5351721985196806187 HTTP 307
  • https://idsync.rlcdn.com/1000.gif?memo=CJ6oGBIeChoIARCUdRoTNTM1MTcyMTk4NTE5NjgwNjE4NxAAGg0Im_ao1QYSBQjoBxAAQgBKAA HTTP 307
  • https://match.adsrvr.org/track/cmf/generic?ttd_pid=liveramp&ttd_tpi=1
Request Chain 257
  • https://cm.g.doubleclick.net/pixel?google_nid=1024&google_cm&google_ula=1641347&party=1&google_hm=NTM1MTcyMTk4NTE5NjgwNjE4Nw&process_consent=T HTTP 302
  • https://c1.adform.net/serving/cookie/match/?party=1&google_gid=CAESEAuus1h_iTVn7AlW2yPNDwU&google_cver=1&google_ula=1641347,0
Request Chain 262
  • https://a.audrte.com/a?adform_uid=5351721985196806187 HTTP 302
  • https://cm.g.doubleclick.net/pixel?google_nid=ar101281&google_hm=bXUzcWxlZXIteHVUYmhaT2pRZmlmUWFhblRvVzJhZy1hZA%3D%3D&gdpr=0&gdpr_consent=&google_redir=https%3A%2F%2Fa.audrte.com%2Fddp%3Fred%3DeyJ1IjoiaHR0cHM6Ly9hLmF1ZHJ0ZS5jb206NDQzL3AiLCJkIjpbXX0%253D%26aruid%3Dmu3qleer-xuTbhZOjQfifQaanToW2ag-ad HTTP 302
  • https://a.audrte.com/ddp?red=eyJ1IjoiaHR0cHM6Ly9hLmF1ZHJ0ZS5jb206NDQzL3AiLCJkIjpbXX0%3D&aruid=mu3qleer-xuTbhZOjQfifQaanToW2ag-ad&gdpr=0&gdpr_consent= HTTP 302
  • https://a.audrte.com/p
Request Chain 263
  • https://dpm.demdex.net/ibs:dpid=1586&dpuuid=5351721985196806187&redir=https%3a%2f%2fc1.adform.net%2fserving%2fcookie%2fmatch%3fparty%3d1007%26cid%3D%24%7BDD_UUID%7D%26noredirect%3D1 HTTP 302
  • https://dpm.demdex.net/demconf.jpg?et:ibs%7cdata:dpid=1586&dpuuid=5351721985196806187&redir=https%3a%2f%2fc1.adform.net%2fserving%2fcookie%2fmatch%3fparty%3d1007%26cid%3D%24%7BDD_UUID%7D%26noredirect%3D1 HTTP 302
  • https://c1.adform.net/serving/cookie/match?party=1007&cid=05182160400965987825571395172295940782&noredirect=1
Request Chain 266
  • https://pm.w55c.net/ping_match.gif?st=adform&rurl=https%3a%2f%2fc1.adform.net%2fserving%2fcookie%2fmatch%3fparty%3d1084%26cid%3D_wfivefivec_ HTTP 302
  • https://pm.w55c.net/ping_match.gif?scc=1&st=adform&rurl=https%3A%2F%2Fc1.adform.net%2Fserving%2Fcookie%2Fmatch%3Fparty%3D1084%26cid%3D_wfivefivec_ HTTP 302
  • https://c1.adform.net/serving/cookie/match?party=1084&cid=F1ff0hWD1X6JoT5
Request Chain 269
  • https://redirect.frontend.weborama.fr/redirect/standard?url=https%3A%2F%2Fc1.adform.net%2Fserving%2Fcookie%2Fmatch%2F%3Fparty%3D1145%26cid%3D%7BWEBO_CID%7D HTTP 307
  • https://redirect.frontend.weborama.fr/redirect/standard?url=https%3A%2F%2Fc1.adform.net%2Fserving%2Fcookie%2Fmatch%2F%3Fparty%3D1145%26cid%3D%7BWEBO_CID%7D&bounce=1&random=3172369169 HTTP 302
  • https://c1.adform.net/serving/cookie/match/?party=1145&cid=7s6MGZXi8VEvDEk4DMJY5e
Request Chain 295
  • https://bbd-tag.de/r/75395-product.js?gdpr=0&gdpr_consent= HTTP 302
  • https://apptracker.stream/r.php?t=75395&p=product&gdpr=0&gdpr_consent=
Request Chain 317
  • https://cm.g.doubleclick.net/pixel?google_nid=tangoomedia&google_ula=7241462486&google_cm&cok15=kwo_dpp_pl&cnty15=POL&t=4&ProgramName=DOPPELHERZ_PL8879&AudienceId=8879&CampaignId=65997&Referrer=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&ProductId=412&ProductCategoryList=Doppelherz%20system&PageType=product&Browsercheck=true&gdpr=0&a15=false&dw15=false&ls15=false HTTP 302
  • https://ban.tangooserver.com/rtb/google/cookiematch.aspx?id=tangoomedia&cok15=kwo_dpp_pl&cnty15=POL&t=4&ProgramName=DOPPELHERZ_PL8879&AudienceId=8879&CampaignId=65997&Referrer=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&ProductId=412&ProductCategoryList=Doppelherz%20system&PageType=product&Browsercheck=true&gdpr=0&a15=false&dw15=false&ls15=false&google_gid=CAESEEiSW-Fd8L3g4FnCSbvue8c&google_cver=1&google_ula=7241462486,0
Request Chain 322
  • https://cm.g.doubleclick.net/pixel?google_nid=preciso_srl&google_ula=6490516189&google_cm&cok15=pne_dpp_pl&cnty15=POL&t=4&ProgramName=DOPPELHERZ_PL&AudienceId=3987&CampaignId=63729&Referrer=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&ProductId=412&ProductCategoryList=Doppelherz%20system&PageType=product&Browsercheck=true&gdpr=0&gdpr_pd=0&a15=false&dw15=false HTTP 302
  • https://ban.2trk.info/rtb/p0n/us6mch?id=p_srl&cok15=pne_dpp_pl&cnty15=POL&t=4&ProgramName=DOPPELHERZ_PL&AudienceId=3987&CampaignId=63729&Referrer=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&ProductId=412&ProductCategoryList=Doppelherz%20system&PageType=product&Browsercheck=true&gdpr=0&gdpr_pd=0&a15=false&dw15=false&google_gid=CAESEPrRQqX8UJgcOMF4Kmq2HUw&google_cver=1&google_ula=6490516189,0

335 HTTP transactions
14 data transactions

Method
Protocol
Status Resource
Path
Size
x-fer
Time
Latency
Type
MIME-Type
IP
Location
GET
H2
200
Primary Request doppelherz-system-kollagen-11000-plus Show response
sklep.doppelherz.pl/
180 KB
36 KB
419ms
277ms
Document
text/html
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
9867a72e13d80f844b2565b31866531b240bba7afec45469b1edf3f808a4d874
Security Headers
Name Value
Strict-Transport-Security max-age=60; includeSubdomains
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

content-encoding
gzip
content-type
text/html; charset="utf-8"
date
Wed, 16 Sep 2026 06:45:44 GMT
server
DCSaaS/httpd
strict-transport-security
max-age=60; includeSubdomains
x-cache-namespace
359593
x-content-type-options
nosniff
x-powered-by
DCSaaS
x-xss-protection
1; mode=block
GET
H2
200
NDc6NTM2OjUuMjYuNDg.css
sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/
429 KB
77 KB
51ms
48ms
Stylesheet
text/css
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
faed7153394c929d9d0faec4ed26f1796b72f819858c48dbbd916e4b16d149e7
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
gzip
etag
"6aa79515-13304"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
content-length
78596
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
text/css
last-modified
Mon, 14 Sep 2026 06:32:53 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
main.ab4429d120a166c61eeb.min.js Show response
sklep.doppelherz.pl/assets/js/frontstore/
967 KB
258 KB
91ms
88ms
Script
application/javascript
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/assets/js/frontstore/main.ab4429d120a166c61eeb.min.js
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
478671d055c158d48c18d24c014fcdc07dabb5ee810c929484774b14315645a2
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
gzip
etag
W/"6aa79505-f1b70"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
application/javascript
last-modified
Mon, 14 Sep 2026 06:32:37 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
pl_PL.js Show response
sklep.doppelherz.pl/userdata/public/locales/
14 KB
5 KB
122ms
119ms
Script
application/javascript
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/userdata/public/locales/pl_PL.js?sci=536
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
0b2451b6ceeca58ad8838ad068a174288107ac1895b597ef13cc3e477ef38a52
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
gzip
etag
W/"6a8c03d0-36cf"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
application/javascript
last-modified
Mon, 24 Aug 2026 08:41:52 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
rwd-custom.woff
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/
5 KB
5 KB
123ms
121ms
Font
font/woff
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/rwd-custom.woff?gptqpz
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
1708f9f0aaeda02b7e0645120d4d17e7e92cbc07c94b648d3c0a250bc61bbad6
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

Origin
https://sklep.doppelherz.pl
sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-1450"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
5200
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
font/woff
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
fontawesome-webfont.woff
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/
43 KB
44 KB
123ms
121ms
Font
font/woff
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/fontawesome-webfont.woff?v=4.0.3
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
0fd28fece9ebd606b8b071460ebd3fc2ed7bc7a66ef91c8834f11dfacab4a849
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

Origin
https://sklep.doppelherz.pl
sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-ad90"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
44432
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
font/woff
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET

aestetico_regular.otf&display=swap
sklep.doppelherz.pl/upload/fonts/
0
0


GET

aestetico_semibold.otf&display=swap
sklep.doppelherz.pl/upload/fonts/
0
0


GET
H2
200
logo.jpg
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/
9 KB
9 KB
131ms
129ms
Image
image/jpeg
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/logo.jpg
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
429413266afc579577d4d13a90a9eb3e29a9637b74c49ed3d6ecc0e6e861edd5
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-220c"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
8716
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/jpeg
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H3
200
front-api-1.5.0.min.js Show response
dcsaascdn.net/js/
10 KB
3 KB
77ms
35ms
Script
application/javascript
104.26.10.75
Cloudflare
General
Full URL
https://dcsaascdn.net/js/front-api-1.5.0.min.js
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.26.10.75 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare / DreamCommerce S.A.
Resource Hash
fe1b2a1d70d5d2c68da5b77054bde21b2e9925bb7b682857abc5bdc1d44a8bbf
Security Headers
Name Value
Strict-Transport-Security max-age=15552000; includeSubDomains; preload
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
cf-cache-status
DYNAMIC
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=DMAZQtlZHqooexIrjkw%2Fp3Ns0%2B0OsQFFQxsTmj4LGZLfYJI%2FhCLmreX9hGJ6KekYxubphx6qFBHcrz4fExpL1nDbMblQrA7lEHSo%2BzjUH%2BRwmgdefkmfUllVK91RJQY%3D"}]}
x-content-type-options
nosniff
access-control-allow-methods
GET, OPTIONS
expires
Fri, 17 Sep 2027 03:30:09 GMT
server-timing
cfExtPri
alt-svc
h3=":443"; ma=86400
date
Wed, 16 Sep 2026 06:45:44 GMT
content-type
application/javascript
last-modified
Tue, 20 May 2025 10:30:05 GMT
vary
accept-encoding
priority
u=3,i=?0
access-control-allow-headers
origin, content-type, accept, x-request, x-requested-with
strict-transport-security
max-age=15552000; includeSubDomains; preload
cache-control
max-age=31622400
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
cf-ray
a3bde8f93c6e980c-WAW
access-control-allow-origin
*
content-length
2369
x-xss-protection
1; mode=block
x-powered-by
DreamCommerce S.A.
x-fmc
1
server
cloudflare
GET
H/1.1
200
OK
4d647c7fbb.js Show response
dfd.doppelherz.pl/js/na/na/u/
17 KB
6 KB
291ms
115ms
Script
application/javascript
95.131.136.1
CLARANET-AS Clara...
General
Full URL
https://dfd.doppelherz.pl/js/na/na/u/4d647c7fbb.js
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_256_GCM
Server
95.131.136.1 , France, ASN8426 (CLARANET-AS Claranet Limited, GB),
Reverse DNS
front.netaffiliation.net
Software
nginx /
Resource Hash
8c3e9e92573cc1a85c0b47b9d062cd2a33cf60f2b46aacf1cf6ac7d36472ccc3

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

Transfer-Encoding
chunked
Content-Encoding
gzip
ETag
W/"6a87f957-459f"
Connection
keep-alive
Date
Wed, 16 Sep 2026 06:45:44 GMT
Content-Type
application/javascript
Last-Modified
Fri, 21 Aug 2026 07:08:07 GMT
Server
nginx
Vary
Accept-Encoding
GET
H3
200
7b75d787-6f54-4376-82da-280ebbba24cf.js Show response
eu1-config.doofinder.com/2.x/
3 KB
2 KB
121ms
54ms
Script
text/javascript
3.174.46.3
Amazon.com
General
Full URL
https://eu1-config.doofinder.com/2.x/7b75d787-6f54-4376-82da-280ebbba24cf.js
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
3.174.46.3 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-174-46-3.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
ed35be425b5c4bdb023df25d8c785e27c94e7284c6c0696074b57b7445bad56a

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding, Origin
cache-control
s-maxage=31536000, max-age=120
content-encoding
br
etag
W/"aea24bf24058107333e4c91df06dd23b"
via
1.1 60b4a5085a39ab80fa3602a95fb5aa9e.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
eV2k5tChchl8iF_rC3yunQ8BtflrP4hAw2qBp7uSWQ4NAglWCzlTPg==
date
Wed, 16 Sep 2026 06:45:44 GMT
content-type
text/javascript
x-amz-cf-pop
FRA60-P12
server
AmazonS3
last-modified
Tue, 15 Sep 2026 13:25:51 GMT
x-amz-server-side-encryption
AES256
GET
H2
200
1px.gif
sklep.doppelherz.pl/libraries/images/
43 B
280 B
131ms
130ms
Image
image/gif
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/libraries/images/1px.gif
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
cf4724b2f736ed1a0ae6bc28f1ead963d9cd2c1fd87b6ef32e7799fc1c5c8bda
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
content-length
43
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/gif
last-modified
Mon, 28 Sep 1970 06:00:00 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
menu_menu.png
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/
148 B
419 B
73ms
71ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/menu_menu.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
88b00559cb3ece9b794d19591ddaa16fca0668d4d41e4707f1b4d1c92f326124
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-94"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
148
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/png
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
menu_search.png
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/
571 B
842 B
89ms
88ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/menu_search.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
de3a7b45086f9561b2d67cf89d988225bac9d1a005b3a28112b342342d011b0e
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-23b"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
571
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/png
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
menu_panel.png
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/
494 B
765 B
98ms
97ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/menu_panel.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
3c33d32ca3c3a71694b27939fb34e90de917438b11bc4b339d0698d904dab910
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-1ee"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
494
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/png
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
menu_basket.png
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/
439 B
710 B
117ms
116ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/menu_basket.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
16bdb2bc2952515ea9f7034108cc922c9b3e5ffa72d643e1551e241edd9cb744
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-1b7"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
439
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/png
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
loader.svg
sklep.doppelherz.pl/libraries/images/
624 B
844 B
118ms
117ms
Image
image/svg+xml
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/libraries/images/loader.svg
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
a5a57a823d4e1d8048e9d9d3f837b3d21ee92b66121727853ead79b16d5542b8
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

etag
"6a9ebc98-270"
x-content-type-options
nosniff
accept-ranges
bytes
content-length
624
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/svg+xml
last-modified
Mon, 07 Sep 2026 13:31:04 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
menu_fav.png
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/
497 B
768 B
118ms
117ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/menu_fav.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
b4d25cac33d1ffae5d09263f4f7b9444061131ce78dc652a989366812b4de2a1
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-1f1"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
497
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/png
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
script Show response
trustmate.io/widget/api/df208cd9-240d-473c-8b8d-16de63da0173/
633 KB
77 KB
251ms
105ms
Script
application/javascript
54.192.35.76
Amazon.com
General
Full URL
https://trustmate.io/widget/api/df208cd9-240d-473c-8b8d-16de63da0173/script
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
54.192.35.76 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-54-192-35-76.fra56.r.cloudfront.net
Software
/
Resource Hash
532dcb7076bdf1d2b249d0266673a1f4913c68b6efaebd5c7d88ac587b33fd0b
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Frame-Options SAMEORIGIN

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
max-age=3600, public
content-encoding
gzip
age
3167
via
1.1 e80e328c1a67b78b31878ecc3bb78c36.cloudfront.net (CloudFront)
expires
Wed, 16 Sep 2026 06:52:57 GMT
access-control-allow-origin
*
x-cache
Hit from cloudfront
x-amz-cf-id
tZH_6f0_vNGkSLZalUSld14sRdX1l6P_-DVD8rPXixdgwN6TkrOxjA==
date
Wed, 16 Sep 2026 05:52:57 GMT
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P15
x-frame-options
SAMEORIGIN
GET
H2
200
script Show response
trustmate.io/widget/api/0acf271b-a747-41cd-84e0-3d83d57d8028/
45 KB
10 KB
307ms
161ms
Script
application/javascript
54.192.35.76
Amazon.com
General
Full URL
https://trustmate.io/widget/api/0acf271b-a747-41cd-84e0-3d83d57d8028/script?product=412
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
54.192.35.76 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-54-192-35-76.fra56.r.cloudfront.net
Software
/
Resource Hash
4f5de075438bd75327e313f024cadadef487c7864a364eebed4c5940bc3b0d55
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Frame-Options SAMEORIGIN

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
max-age=3600, public
content-encoding
gzip
age
1334
via
1.1 e80e328c1a67b78b31878ecc3bb78c36.cloudfront.net (CloudFront)
expires
Wed, 16 Sep 2026 07:23:30 GMT
access-control-allow-origin
*
x-cache
Hit from cloudfront
x-amz-cf-id
XRk-AZU737aKbP_J5pcdK8QHPQoot9Ztwc0EGLjzubPBrrEHghQKAg==
date
Wed, 16 Sep 2026 06:23:30 GMT
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P15
x-frame-options
SAMEORIGIN
GET
H2
200
Doppelherz-system-Kollagen-11.000-PLUS%2C-30-ampulek-po-25ml.png
sklep.doppelherz.pl/environment/cache/images/productGfx_1199_500_500/
149 KB
149 KB
117ms
116ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/environment/cache/images/productGfx_1199_500_500/Doppelherz-system-Kollagen-11.000-PLUS%2C-30-ampulek-po-25ml.png?overlay=1
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
dce698380cf451415db4698d5005ae4f287cbbcf70771e19e4997b4ad7663367
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000
etag
8be626fb43b8263c87ed2223838f5446
x-content-type-options
nosniff
accept-ranges
bytes
content-length
152414
date
Wed, 16 Sep 2026 06:45:44 GMT
content-type
image/png
last-modified
Mon, 17 Aug 2026 18:05:32 GMT
server
DCSaaS/httpd
x-powered-by
DCSaaS
GET
H2
200
Doppelherz-system-Kollagen-11.000-PLUS%2C-30-ampulek-po-25ml.png
sklep.doppelherz.pl/environment/cache/images/productGfx_1199_120_120/
15 KB
15 KB
99ms
98ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/environment/cache/images/productGfx_1199_120_120/Doppelherz-system-Kollagen-11.000-PLUS%2C-30-ampulek-po-25ml.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
517a673d22e83eacdb62bef3b37e4d957e6ecd73ba590426da1656213560ec30
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000
etag
0924549560b0cb8e16ff655ca3eb64bb
x-content-type-options
nosniff
accept-ranges
bytes
content-length
15546
date
Wed, 16 Sep 2026 06:45:44 GMT
content-type
image/png
last-modified
Mon, 17 Aug 2026 18:09:02 GMT
server
DCSaaS/httpd
x-powered-by
DCSaaS
GET
H2
200
Kolagen-do-picia.jpg
sklep.doppelherz.pl/environment/cache/images/productGfx_591_120_120/
5 KB
5 KB
100ms
99ms
Image
image/jpeg
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/environment/cache/images/productGfx_591_120_120/Kolagen-do-picia.jpg
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
fd988db891a09dcd2b69471bf1195994a2bf966e9c4f716e5fdd49b9ae8398cd
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000
etag
0b8c24dac478d7992979f24b9339d65e
x-content-type-options
nosniff
accept-ranges
bytes
content-length
4644
date
Wed, 16 Sep 2026 06:45:44 GMT
content-type
image/jpeg
last-modified
Mon, 17 Aug 2026 18:05:32 GMT
server
DCSaaS/httpd
x-powered-by
DCSaaS
GET
H2
200
Kolagen-do-picia.png
sklep.doppelherz.pl/environment/cache/images/productGfx_641_120_120/
12 KB
12 KB
102ms
101ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/environment/cache/images/productGfx_641_120_120/Kolagen-do-picia.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
01d5a4b445e0523715bc8f1062e7efdc2473b2d09b084a70f4c1d9676d52515e
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000
etag
e323beffe9d85cfde9bd7391223ce258
x-content-type-options
nosniff
accept-ranges
bytes
content-length
12378
date
Wed, 16 Sep 2026 06:45:44 GMT
content-type
image/png
last-modified
Mon, 17 Aug 2026 18:05:32 GMT
server
DCSaaS/httpd
x-powered-by
DCSaaS
GET
H2
200
Kolagen-do-picia.png
sklep.doppelherz.pl/environment/cache/images/productGfx_639_120_120/
11 KB
11 KB
113ms
113ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/environment/cache/images/productGfx_639_120_120/Kolagen-do-picia.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
efe1fffde0e6048ed59531c1ef360bc6970620d39e97db8d6b20cbd252c669f8
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000
etag
ae6f463268a2f93e52a7c8c916c9ff9b
x-content-type-options
nosniff
accept-ranges
bytes
content-length
11171
date
Wed, 16 Sep 2026 06:45:44 GMT
content-type
image/png
last-modified
Mon, 17 Aug 2026 18:05:32 GMT
server
DCSaaS/httpd
x-powered-by
DCSaaS
GET
H2
200
Kolagen-do-picia.webp
sklep.doppelherz.pl/environment/cache/images/productGfx_1152_120_120/
4 KB
4 KB
103ms
102ms
Image
image/webp
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/environment/cache/images/productGfx_1152_120_120/Kolagen-do-picia.webp
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
49c1cee0872913c07429752eb0a6c8304cda60c775ad28c47005114754dbbc2d
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000
etag
9dca72ce71e5b2ab8c4851884757d580
x-content-type-options
nosniff
accept-ranges
bytes
content-length
3680
date
Wed, 16 Sep 2026 06:45:44 GMT
content-type
image/webp
last-modified
Mon, 17 Aug 2026 18:05:32 GMT
server
DCSaaS/httpd
x-powered-by
DCSaaS
GET
H2
200
Kolagen-do-picia.png
sklep.doppelherz.pl/environment/cache/images/productGfx_640_120_120/
20 KB
20 KB
116ms
115ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/environment/cache/images/productGfx_640_120_120/Kolagen-do-picia.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
494308d422e33784eaa98d5027d01e9774b731928114817a632688e890e3e287
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000
etag
09355e91a1eac5be1f4e15e830a52870
x-content-type-options
nosniff
accept-ranges
bytes
content-length
20384
date
Wed, 16 Sep 2026 06:45:44 GMT
content-type
image/png
last-modified
Mon, 17 Aug 2026 18:05:32 GMT
server
DCSaaS/httpd
x-powered-by
DCSaaS
GET
H2
200
Doppelherz-system-Kollagen-11000-Sklep-Doppelherz.jpg
sklep.doppelherz.pl/environment/cache/images/productGfx_263_120_120/
5 KB
5 KB
103ms
103ms
Image
image/jpeg
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/environment/cache/images/productGfx_263_120_120/Doppelherz-system-Kollagen-11000-Sklep-Doppelherz.jpg
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
5fcac030d205e29a1f983dff90e05178f8daf61e948c3abdc1dd862d09765b99
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000
etag
d2a3e937146facd042bf5286d1982ba2
x-content-type-options
nosniff
accept-ranges
bytes
content-length
5274
date
Wed, 16 Sep 2026 06:45:44 GMT
content-type
image/jpeg
last-modified
Mon, 17 Aug 2026 18:05:32 GMT
server
DCSaaS/httpd
x-powered-by
DCSaaS
GET
H2
200
Doppelherz-system-Kollagen-11.000-PLUS%2C-30-ampulek-po-25ml.png
sklep.doppelherz.pl/userdata/public/gfx/1199/
475 KB
475 KB
193ms
192ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/userdata/public/gfx/1199/Doppelherz-system-Kollagen-11.000-PLUS%2C-30-ampulek-po-25ml.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
79de2ef4fdda9dbb87fe609306bf5d6b3599f538c1202f8e06500eec9f70c002
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000
etag
9ed9782832dc1bab29d1142a9c6c16a1
x-cdn
1
x-content-type-options
nosniff
accept-ranges
bytes
content-length
485977
date
Wed, 16 Sep 2026 06:45:44 GMT
content-type
image/png
last-modified
Wed, 20 May 2026 15:32:30 GMT
server
DCSaaS/httpd
x-powered-by
DCSaaS
GET
H2
200
add_to_fav.png
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/
475 B
746 B
116ms
116ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/add_to_fav.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
825610ec409015e347107df643e38e29ea1b7f7fb02bd61b8f1a1f8463859049
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-1db"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
475
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/png
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
639.png
sklep.doppelherz.pl/userdata/public/assets/w%C5%82asne/karty/
128 KB
128 KB
132ms
131ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/userdata/public/assets/w%C5%82asne/karty/639.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
3a91a95c37ebab405756cd9475169f4483af9a5dea8a3941a2915d7c363eeecb
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6818c83c-1ff89"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
130953
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/png
last-modified
Mon, 05 May 2025 14:16:28 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
Kolagen-do-picia%20%2813%29.webp
sklep.doppelherz.pl/userdata/public/assets/w%C5%82asne/karty/
52 KB
53 KB
117ms
116ms
Image
image/webp
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/userdata/public/assets/w%C5%82asne/karty/Kolagen-do-picia%20%2813%29.webp
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
4f8006ce48b56bdab84857e288b79f980d6c3243909010760b231005a367322e
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"69b2d09d-d148"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
53576
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/webp
last-modified
Thu, 12 Mar 2026 14:41:33 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
133023_Doppelherz_Kollagen_.jpg
sklep.doppelherz.pl/userdata/public/assets/w%C5%82asne/
29 KB
29 KB
132ms
132ms
Image
image/jpeg
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/userdata/public/assets/w%C5%82asne/133023_Doppelherz_Kollagen_.jpg
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
3ca724904d4393807243f6f6aff87f2c6652de1486708a02e42b1a7e86d2d7d2
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6298c2e5-73f8"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
29688
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/jpeg
last-modified
Thu, 02 Jun 2022 14:02:13 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
script Show response
trustmate.io/widget/api/1928d3f4-a6ef-4402-a7d7-247ba5e6e1d5/
531 KB
75 KB
308ms
166ms
Script
application/javascript
54.192.35.76
Amazon.com
General
Full URL
https://trustmate.io/widget/api/1928d3f4-a6ef-4402-a7d7-247ba5e6e1d5/script?product=412
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
54.192.35.76 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-54-192-35-76.fra56.r.cloudfront.net
Software
/
Resource Hash
d7f8473a05febc55f00d282ee211a745afe54dda9732fb11b4d1e8e6f3a3adf5
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Frame-Options SAMEORIGIN

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
max-age=3600, public
content-encoding
gzip
age
1334
via
1.1 e80e328c1a67b78b31878ecc3bb78c36.cloudfront.net (CloudFront)
expires
Wed, 16 Sep 2026 07:23:30 GMT
access-control-allow-origin
*
x-cache
Hit from cloudfront
x-amz-cf-id
5wB8kvVb_VSwTv5auObiOkIdnzq5i-Yn41bg990-9ThXm06s71XAuw==
date
Wed, 16 Sep 2026 06:23:30 GMT
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P15
x-frame-options
SAMEORIGIN
GET
H3
200
mustache.min.js Show response
cdnjs.cloudflare.com/ajax/libs/mustache.js/2.3.0/
9 KB
3 KB
72ms
40ms
Script
application/javascript
104.17.24.14
Cloudflare
General
Full URL
https://cdnjs.cloudflare.com/ajax/libs/mustache.js/2.3.0/mustache.min.js
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.17.24.14 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
89aa9f3b9b9ed156d219c122427f8e797c67c4030adbe4201d72030396d6b462
Security Headers
Name Value
Strict-Transport-Security max-age=15780000
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cf-cdnjs-via
cfworker/r2
content-encoding
br
cf-cache-status
BYPASS
age
1285340
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=%2FLmr7e7D8G91tcmzAcWa20rveM11w%2BULUuhjDYvhC8OxO%2FKMKxYRAC8SZ%2Bl%2F1uG%2BAeOqMiJb38%2BKlsxPbAV%2Brj7MwsVVXCc7rPpWFzt9BJ9iKKYjmU7rRqVppqdtSrhGeVQ501%2Bv"}]}
x-content-type-options
nosniff
server-timing
cfExtPri
alt-svc
h3=":443"; ma=86400
x-cdnjs-cache
HIT
date
Wed, 16 Sep 2026 06:45:44 GMT
content-type
application/javascript; charset=utf-8
last-modified
Mon, 04 May 2020 16:13:29 GMT
vary
Accept-Encoding
priority
u=2,i=?0
strict-transport-security
max-age=15780000
cache-control
no-transform, public, s-maxage=30672000, max-age=30672000, immutable
timing-allow-origin
*
nel
{"report_to":"cf-nel","success_fraction":0.01,"max_age":604800}
cross-origin-resource-policy
cross-origin
cf-ray
a3bde8f94e16b812-WAW
access-control-allow-origin
*
content-length
2513
server
cloudflare
GET
H2
200
DHxFCB.svg
sklep.doppelherz.pl/userdata/public/assets/icons/
823 KB
825 KB
146ms
145ms
Image
image/svg+xml
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/userdata/public/assets/icons/DHxFCB.svg
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
282e4d6eaed8b34d6cf4e48e09433dfe98d41cd02a4dbe4111e5c64859ecf76a
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

etag
"68790aef-cdc0a"
x-content-type-options
nosniff
accept-ranges
bytes
content-length
842762
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/svg+xml
last-modified
Thu, 17 Jul 2025 14:38:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
script Show response
trustmate.io/widget/api/bc5abbfe-277a-4b98-8b9f-9b8f3509207c/
60 KB
17 KB
245ms
105ms
Script
application/javascript
54.192.35.76
Amazon.com
General
Full URL
https://trustmate.io/widget/api/bc5abbfe-277a-4b98-8b9f-9b8f3509207c/script
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
54.192.35.76 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-54-192-35-76.fra56.r.cloudfront.net
Software
/
Resource Hash
78fef654fe4087e4f21039ddda38ad941c5b7ca86e557ccf7e390852f0dcd0d6
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Frame-Options SAMEORIGIN

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
max-age=3600, public
content-encoding
gzip
age
1764
via
1.1 e80e328c1a67b78b31878ecc3bb78c36.cloudfront.net (CloudFront)
expires
Wed, 16 Sep 2026 07:16:20 GMT
access-control-allow-origin
*
x-cache
Hit from cloudfront
x-amz-cf-id
rl3mHwVrdtuI2HhhUcwHBGeK4YEKPWP3fLtByXSJzouzz3NCu2wkIg==
date
Wed, 16 Sep 2026 06:16:20 GMT
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P15
x-frame-options
SAMEORIGIN
GET
H2
200
footer_facebook.svg
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/
427 B
702 B
148ms
147ms
Image
image/svg+xml
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/footer_facebook.svg
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
5bad2c32517cf14baa185e75a0f27d25b9d1dfa75317cc739be7177d444a8b81
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-1ab"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
427
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/svg+xml
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
footer_instagram.svg
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/
2 KB
2 KB
150ms
149ms
Image
image/svg+xml
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/footer_instagram.svg
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
d59bed3d53c4e63f3358774eb4537017ad90da5a4fcbae205dd8880fa625a65e
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-6dc"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
1756
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/svg+xml
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
footer_youtube.svg
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/
468 B
743 B
132ms
131ms
Image
image/svg+xml
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/footer_youtube.svg
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
d291f83b76832e96aacd958217ede0f2309904c18366e326b2e20d9588a3ae3e
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-1d4"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
468
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/svg+xml
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
footer_heart.png
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/
376 B
647 B
133ms
132ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/footer_heart.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
cb3f2fd3ae3327535a435ad6416fb4dad5192fa841384e370d32d03b2b40ff19
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-178"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
376
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/png
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
usernodefer.js Show response
sklep.doppelherz.pl/skins/user/rwd_shoper_42/js/
5 KB
2 KB
133ms
133ms
Script
application/javascript
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/js/usernodefer.js
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
f99a2313e266466791ecfd25934d97b1364fbac993822367d46ffeb0fae2263b
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
gzip
etag
W/"6aa0f517-141e"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
application/javascript
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
user.js Show response
sklep.doppelherz.pl/skins/user/rwd_shoper_42/js/
111 KB
26 KB
186ms
186ms
Script
application/javascript
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/js/user.js?sci=536
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
27e40039731c83667839dd239bbe6f1f6108925bd8cb9aafd6794cd46903f11c
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
content-encoding
gzip
etag
W/"6aa3d3b4-1bd39"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
application/javascript
last-modified
Fri, 11 Sep 2026 10:11:00 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
platform.js Show response
apis.google.com/js/
63 KB
25 KB
213ms
75ms
Script
text/javascript
142.251.14.101
Google LLC
General
Full URL
https://apis.google.com/js/platform.js?onload=renderBadge
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.14.101 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f101.1e100.net
Software
sffe /
Resource Hash
eb2298c95a2861580ba717af6124123498f81414b6830952fca9d7d5b6bdaf97
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/gapi-team
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
"3971a17915cfff7c"
report-to
{"group":"gapi-team","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/gapi-team"}]}
x-content-type-options
nosniff
expires
Wed, 16 Sep 2026 06:45:44 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 16 Sep 2026 06:45:44 GMT
content-type
text/javascript
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/gapi-team
cache-control
private, max-age=1800, stale-while-revalidate=1800
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="gapi-team"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
content-length
24732
x-xss-protection
0
server
sffe
GET
H2
200
Shortcode.js Show response
cdn.appstore.mamezi.pl/libs/shortcode/src/
4 KB
2 KB
280ms
103ms
Script
application/javascript
65.8.131.85
Amazon.com
General
Full URL
https://cdn.appstore.mamezi.pl/libs/shortcode/src/Shortcode.js?v=20260914141711
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
65.8.131.85 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-65-8-131-85.fra60.r.cloudfront.net
Software
Apache/2 /
Resource Hash
913512af2ec36b2c6b44baa5d5645e05f218c22cbad303fcbdf4fb162427db99

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
"e44-5a5705fe02ac0-gzip"
age
152872
expires
Wed, 14 Oct 2026 12:17:52 GMT
x-cache
Hit from cloudfront
x-amz-cf-id
Y2yxjCmgpbWLosscLJ-GnK_tmNlYDwGGCtia5v8q4BXn8EYJq5M4Dw==
date
Mon, 14 Sep 2026 12:17:52 GMT
content-type
application/javascript
last-modified
Tue, 12 May 2020 09:49:07 GMT
vary
Accept-Encoding
cache-control
max-age=4838400, public
via
1.1 c8441ee313b5204aa32e9bf5a370d536.cloudfront.net (CloudFront)
accept-ranges
bytes
content-length
1552
x-amz-cf-pop
FRA60-P13
server
Apache/2
GET
H2
200
mamezi_boxy_produktowe.js Show response
cdn.appstore.mamezi.pl/boxy_produktowe/
18 KB
6 KB
203ms
80ms
Script
text/javascript
65.8.131.85
Amazon.com
General
Full URL
https://cdn.appstore.mamezi.pl/boxy_produktowe/mamezi_boxy_produktowe.js?shop=a96db86b9d7d6d7f128220325e99fe925c001520&v=20260914141711
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
65.8.131.85 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-65-8-131-85.fra60.r.cloudfront.net
Software
Apache/2 / PHP/7.4.33
Resource Hash
0ec1b2f1d5d75d1c7cbd1af2a58148327d1cd75ca49316ebfb1a1857bc7786d1

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000
content-encoding
gzip
age
152872
via
1.1 c8441ee313b5204aa32e9bf5a370d536.cloudfront.net (CloudFront)
expires
Wed, 14 Oct 2026 12:17:52 GMT
x-cache
Hit from cloudfront
content-length
5634
x-amz-cf-id
35GtajkNV3PqqPWDWujKxtl-7gENjRnTLUqvsoGe3kXx8xmEWfPN6g==
date
Mon, 14 Sep 2026 12:17:52 GMT
content-type
text/javascript;charset=UTF-8
x-powered-by
PHP/7.4.33
server
Apache/2
x-amz-cf-pop
FRA60-P13
vary
Accept-Encoding
GET
H2
200
8043ca46-dfdc-4448-9ae4-77ff9c78a5bc.js Show response
papi.trustmate.io/shoper/widget/shop/
17 KB
5 KB
226ms
81ms
Script
application/javascript
18.198.138.71
Amazon.com
General
Full URL
https://papi.trustmate.io/shoper/widget/shop/8043ca46-dfdc-4448-9ae4-77ff9c78a5bc.js
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
18.198.138.71 Frankfurt am Main, Germany, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-18-198-138-71.eu-central-1.compute.amazonaws.com
Software
/
Resource Hash
a3eab44faae5ebfa71bb638c643fff0c6db138c2125fdc8bea8cac41039636aa
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
public, max-age=60
content-encoding
gzip
cross-origin-opener-policy
same-origin
x-content-type-options
nosniff
referrer-policy
same-origin
access-control-allow-origin
*
content-length
4559
date
Wed, 16 Sep 2026 06:45:44 GMT
x-trustmate-cache
hit
content-type
application/javascript
vary
Accept-Encoding
x-xss-protection
1; mode=block
GET
H2
200
mamezi_produkty_powiazane.js Show response
cdn.appstore.mamezi.pl/wariantykol/
5 KB
2 KB
155ms
76ms
Script
text/javascript
65.8.131.85
Amazon.com
General
Full URL
https://cdn.appstore.mamezi.pl/wariantykol/mamezi_produkty_powiazane.js?shop=a96db86b9d7d6d7f128220325e99fe925c001520&v=20260105112839
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
65.8.131.85 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-65-8-131-85.fra60.r.cloudfront.net
Software
Apache/2 / PHP/7.4.33
Resource Hash
d1960e3210bb571e5a0f2d01c2f0c9be536122a4f886c21e78db67713cbba246

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000
content-encoding
gzip
age
436911
via
1.1 c8441ee313b5204aa32e9bf5a370d536.cloudfront.net (CloudFront)
expires
Sun, 11 Oct 2026 05:23:53 GMT
x-cache
Hit from cloudfront
content-length
1815
x-amz-cf-id
YtkyUUxSRtcKYD_2ao0gvUxEa_-HqRdbl1bKBDF7tzw0Sg9GX31s4Q==
date
Fri, 11 Sep 2026 05:23:53 GMT
content-type
text/javascript;charset=utf-8
x-powered-by
PHP/7.4.33
server
Apache/2
x-amz-cf-pop
FRA60-P13
vary
Accept-Encoding
GET
H2
200
gtm.js Show response
www.googletagmanager.com/
574 KB
181 KB
218ms
89ms
Script
application/javascript
192.178.183.97
Google LLC
General
Full URL
https://www.googletagmanager.com/gtm.js?id=GTM-MBRKD4N
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
192.178.183.97 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfraw-in-f97.1e100.net
Software
Google Tag Manager /
Resource Hash
b2e9c4b1b79bcb2769410bc28f0a690d1cb508d20b3acb46bb4c0657ce62392c
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
zstd
expires
Wed, 16 Sep 2026 06:45:44 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 16 Sep 2026 06:45:44 GMT
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
last-modified
Wed, 16 Sep 2026 06:00:00 GMT
access-control-allow-headers
Cache-Control
strict-transport-security
max-age=31536000; includeSubDomains
cache-control
private, max-age=900
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
access-control-allow-origin
*
content-length
184695
x-xss-protection
0
server
Google Tag Manager
GET
H2
200
script.js Show response
ssl.ceneo.pl/ct/v5/
4 KB
3 KB
290ms
135ms
Script
application/javascript
185.31.26.219
QXL-POLAND Allegr...
General
Full URL
https://ssl.ceneo.pl/ct/v5/script.js?accountGuid=967ae452-dc22-484a-b939-e8d3667c6082&t=1789541144745&dl=dataLayer
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
185.31.26.219 , Poland, ASN42656 (QXL-POLAND Allegro sp. z o.o., PL),
Reverse DNS
Software
/
Resource Hash
19ec38dda2432d729e75c2c02c3b3ef83aae74029871cdf496d58f0c1b2a942d
Security Headers
Name Value
Content-Security-Policy default-src * 'unsafe-inline' 'unsafe-eval'; img-src * data:
Strict-Transport-Security max-age=10886400; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=10886400; includeSubDomains; preload
content-security-policy
default-src * 'unsafe-inline' 'unsafe-eval'; img-src * data:
cache-control
public,max-age=600
content-encoding
gzip
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
x-content-type-options
nosniff
referrer-policy
no-referrer-when-downgrade
request-context
appId=cid-v1:c6d2b834-9961-40f1-94ff-46263261adeb
permissions-policy
accelerometer=(), camera=(), geolocation=(), gyroscope=(), magnetometer=(), microphone=(), payment=(), usb=()
access-control-allow-origin
*
date
Wed, 16 Sep 2026 06:45:44 GMT
content-type
application/javascript
vary
Accept-Encoding
access-control-allow-headers
*
GET
H2
200
tr.js Show response
pixel.wp.pl/w/
54 KB
55 KB
100ms
32ms
Script
application/javascript
212.77.113.26
WirtualnaPolska W...
General
Full URL
https://pixel.wp.pl/w/tr.js
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
212.77.113.26 , Poland, ASN12827 (WirtualnaPolska Wirtualna Polska Media S.A., PL),
Reverse DNS
Software
nginx /
Resource Hash
ed31b8cee3cce1b2d13f51ad332d9f8a9264cc415832fa8be45f285caa76a26d

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-store
etag
"6aa929e6-d9bf"
accept-ch
device-memory, dpr, width, viewport-width, rtt, downlink, ect, sec-ch-ua, sec-ch-ua-platform, sec-ch-ua-mobile, sec-ch-ua-full-version-list, sec-ch-ua-platform-version, sec-ch-ua-arch, sec-ch-ua-bitness, sec-ch-ua-model
access-control-allow-credentials
true
x-op-id-all
1a1r1d
accept-ch-lifetime
604800
accept-ranges
bytes
content-length
55743
date
Wed, 16 Sep 2026 06:45:44 GMT
content-type
application/javascript
last-modified
Tue, 15 Sep 2026 11:20:06 GMT
server
nginx
GET
H2
200
RIenpVjeLR8 Show response
www.youtube.com/embed/ Frame 90C8
154 KB
64 KB
231ms
128ms
Document
text/html
142.251.156.4
Google LLC
General
Full URL
https://www.youtube.com/embed/RIenpVjeLR8?si=BHrZAFVtmPsydAwu
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.156.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
06778826e14e51d6211800d4fa8b7a6db32a58d0a05f72acd87a2bbab0b9328d
Security Headers
Name Value
Content-Security-Policy script-src 'unsafe-eval' 'self' 'unsafe-inline' https://www.google.com https://apis.google.com https://ssl.gstatic.com https://www.gstatic.com https://www.googletagmanager.com https://www.google-analytics.com https://*.youtube.com https://*.google.com https://*.gstatic.com https://youtube.com https://www.youtube.com https://google.com https://*.doubleclick.net https://*.googleapis.com https://www.googleadservices.com https://tpc.googlesyndication.com https://www.youtubekids.com https://www.youtube-nocookie.com https://www.youtubeeducation.com https://www-onepick-opensocial.googleusercontent.com;report-uri https://csp.withgoogle.com/csp/youtube_main/allowlist require-trusted-types-for 'script' base-uri 'self';object-src 'none';script-src 'report-sample' 'nonce-jo9_wjBXX2ptAOBKdGodvg' 'unsafe-inline' 'strict-dynamic' https: http: 'unsafe-eval';report-uri https://csp.withgoogle.com/csp/youtube_main/strict
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://sklep.doppelherz.pl/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cache-control
no-cache, no-store, max-age=0, must-revalidate
content-encoding
br
content-security-policy
script-src 'unsafe-eval' 'self' 'unsafe-inline' https://www.google.com https://apis.google.com https://ssl.gstatic.com https://www.gstatic.com https://www.googletagmanager.com https://www.google-analytics.com https://*.youtube.com https://*.google.com https://*.gstatic.com https://youtube.com https://www.youtube.com https://google.com https://*.doubleclick.net https://*.googleapis.com https://www.googleadservices.com https://tpc.googlesyndication.com https://www.youtubekids.com https://www.youtube-nocookie.com https://www.youtubeeducation.com https://www-onepick-opensocial.googleusercontent.com;report-uri https://csp.withgoogle.com/csp/youtube_main/allowlist require-trusted-types-for 'script' base-uri 'self';object-src 'none';script-src 'report-sample' 'nonce-jo9_wjBXX2ptAOBKdGodvg' 'unsafe-inline' 'strict-dynamic' https: http: 'unsafe-eval';report-uri https://csp.withgoogle.com/csp/youtube_main/strict
content-type
text/html; charset=utf-8
cross-origin-embedder-policy-report-only
require-corp; report-to="youtube_main"
cross-origin-opener-policy-report-only
same-origin; report-to="youtube_main"
cross-origin-resource-policy
cross-origin
date
Wed, 16 Sep 2026 06:45:44 GMT
expires
Mon, 01 Jan 1990 00:00:00 GMT
origin-trial
AmhMBR6zCLzDDxpW+HfpP67BqwIknWnyMOXOQGfzYswFmJe+fgaI6XZgAzcxOrzNtP7hEDsOo1jdjFnVr2IdxQ4AAAB4eyJvcmlnaW4iOiJodHRwczovL3lvdXR1YmUuY29tOjQ0MyIsImZlYXR1cmUiOiJXZWJWaWV3WFJlcXVlc3RlZFdpdGhEZXByZWNhdGlvbiIsImV4cGlyeSI6MTc1ODA2NzE5OSwiaXNTdWJkb21haW4iOnRydWV9 AiDEBptUfVeO93q48VdVMe/ubupazdAl8AaHP+NBzdnW8quUcHdzJUyGSfrmtpKJu7EOvwRp9ug2rEo3XU+WMAMAAAB2eyJvcmlnaW4iOiJodHRwczovL3lvdXR1YmUuY29tOjQ0MyIsImZlYXR1cmUiOiJEZXZpY2VCb3VuZFNlc3Npb25DcmVkZW50aWFsczIiLCJleHBpcnkiOjE3NzQzMTA0MDAsImlzU3ViZG9tYWluIjp0cnVlfQ==
p3p
CP="This is not a P3P policy! See http://support.google.com/accounts/answer/151657?hl=pl for more info."
permissions-policy
ch-ua-arch=*, ch-ua-bitness=*, ch-ua-full-version=*, ch-ua-full-version-list=*, ch-ua-model=*, ch-ua-wow64=*, ch-ua-form-factors=*, ch-ua-platform=*, ch-ua-platform-version=*
pragma
no-cache
report-to
{"group":"youtube_main","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube_main"}]}
server
ESF
strict-transport-security
max-age=31536000
vary
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
x-content-type-options
nosniff
x-xss-protection
0
GET
DATA
200
OK
truncated
/
26 B
0
Image
image/gif

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
3b7b8a4b411ddf8db9bacc2f3aabf406f8e4c0c087829b336ca331c40adfdff1

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/gif
GET
H2
200
412 Show response
sklep.doppelherz.pl/webapi/front/pl_PL/products/PLN/
16 KB
5 KB
64ms
63ms
XHR
application/json
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/webapi/front/pl_PL/products/PLN/412
Requested by
Host: dcsaascdn.net
URL: https://dcsaascdn.net/js/front-api-1.5.0.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
3ed35cf9ad778c757574790425fbb79599fddf51120beae4b862fd847c18946f
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-content-type-options
nosniff
content-length
5099
date
Wed, 16 Sep 2026 06:45:44 GMT
content-type
application/json
x-powered-by
DCSaaS
x-fmc
5
server
DCSaaS/httpd
GET
H2
200
072fe22_front.js Show response
pprzesylka.maxsote.pl/mxfcache/frontjs/
76 KB
17 KB
215ms
81ms
Fetch
application/javascript
185.41.71.25
AS-HITME Marek Ba...
General
Full URL
https://pprzesylka.maxsote.pl/mxfcache/frontjs/072fe22_front.js?m1779711788
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , CHACHA20_POLY1305
Server
185.41.71.25 , Poland, ASN50840 (AS-HITME Marek Bajerski trading as HITME.PL, PL),
Reverse DNS
dapro1836.serwervps.pl
Software
/
Resource Hash
9f071f1ca8abaeac147a749be1063dd6b1b5b1a2e7f1d45bae67ad94e36ce16e

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
public, max-age=604800
content-encoding
br
etag
"130b7-6aaa1ed1-31a9908472778f93;br"
expires
Wed, 23 Sep 2026 06:45:44 GMT
accept-ranges
bytes
access-control-allow-origin
*
content-length
17111
date
Wed, 16 Sep 2026 06:45:44 GMT
content-type
application/javascript
last-modified
Wed, 16 Sep 2026 04:45:05 GMT
vary
Accept-Encoding,User-Agent
GET
H2
200
get_code.php Show response
mxapp4.maxserver.pl/appProduktGratisowy/
1 MB
744 KB
675ms
542ms
XHR
text/html
185.41.68.192
AS-HITME Marek Ba...
General
Full URL
https://mxapp4.maxserver.pl/appProduktGratisowy/get_code.php?id=682&m=1789038339
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/assets/js/frontstore/main.ab4429d120a166c61eeb.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
185.41.68.192 , Poland, ASN50840 (AS-HITME Marek Bajerski trading as HITME.PL, PL),
Reverse DNS
hybryda18837.hitme.net.pl
Software
Apache/2 /
Resource Hash
ddf6e17bb70a67b80c1a6f4bba1f53ac7373589e3387aa416b957b573398979e
Security Headers
Name Value
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Accept
*/*
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=86400
content-encoding
gzip
pragma
cache
expires
Thu, 17 Sep 2026 06:45:44 GMT, Thu, 15 Apr 2020 20:00:00 GMT
access-control-allow-origin
*
x-xss-protection
1; mode=block
date
Wed, 16 Sep 2026 06:45:44 GMT
content-type
text/html; charset=UTF-8
vary
Accept-Encoding,User-Agent
server
Apache/2
GET
H2
200
get_code.php Show response
mxapp4.maxserver.pl/appPromocjaDwaplusJeden/
0
289 B
238ms
105ms
XHR
text/html
185.41.68.192
AS-HITME Marek Ba...
General
Full URL
https://mxapp4.maxserver.pl/appPromocjaDwaplusJeden/get_code.php?id=871&m=1746797718
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/assets/js/frontstore/main.ab4429d120a166c61eeb.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
185.41.68.192 , Poland, ASN50840 (AS-HITME Marek Bajerski trading as HITME.PL, PL),
Reverse DNS
hybryda18837.hitme.net.pl
Software
Apache/2 /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Accept
*/*
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=86400
pragma
cache
expires
Thu, 17 Sep 2026 06:45:44 GMT, Thu, 15 Apr 2020 20:00:00 GMT
access-control-allow-origin
*
content-length
0
x-xss-protection
1; mode=block
date
Wed, 16 Sep 2026 06:45:44 GMT
content-type
text/html; charset=UTF-8
vary
Referer,User-Agent
server
Apache/2
GET
H2
200
mamezi_boxy_produktowe.css
cdn.appstore.mamezi.pl/boxy_produktowe/
4 KB
1 KB
88ms
87ms
Stylesheet
text/css
65.8.131.85
Amazon.com
General
Full URL
https://cdn.appstore.mamezi.pl/boxy_produktowe/mamezi_boxy_produktowe.css?v=20260914141711
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
65.8.131.85 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-65-8-131-85.fra60.r.cloudfront.net
Software
Apache/2 /
Resource Hash
aac07ec04684c78e426aeff7bb5fbba1a807abe0293a679f6c47ec3d0e66a4a2

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
"10ed-6085f44cbcb1e-gzip"
age
152871
expires
Wed, 14 Oct 2026 12:17:53 GMT
x-cache
Hit from cloudfront
x-amz-cf-id
jfBePSbJrLUM74dhUqNTQ9bTcxZBo6qo6OD9FlL4oLQNu6WonzmlyA==
date
Mon, 14 Sep 2026 12:17:53 GMT
content-type
text/css
last-modified
Mon, 23 Oct 2023 09:58:49 GMT
vary
Accept-Encoding
cache-control
max-age=4838400, public
via
1.1 c8441ee313b5204aa32e9bf5a370d536.cloudfront.net (CloudFront)
accept-ranges
bytes
content-length
906
x-amz-cf-pop
FRA60-P13
server
Apache/2
GET

script.php
hotinfo.maxserver.pl/appHotbasket/
0
0


GET
H2
200
btn_chev_b.png
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/
237 B
508 B
64ms
63ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/btn_chev_b.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
d653f70eae4794386d3171660113acfa6bf1a78e32fb26c53ffca6b1701537dc
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-ed"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
237
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/png
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
btn_arrow_b.png
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/
307 B
578 B
63ms
62ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/btn_arrow_b.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
dbf653f04084c779b785ea88cd2792e5436a3bd320d0e7588545412233103c01
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-133"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
307
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/png
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
search_btn.png
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/
456 B
727 B
64ms
61ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/search_btn.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
eeb02e62df4875965ff9c2bcd9ba29e6139289375059e9fc714cf5ab90ae6837
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-1c8"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
456
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/png
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
melem_back.png
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/
275 B
546 B
64ms
62ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/melem_back.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
55f37deb8b81275f66bfbb386c9700f74b06dca4111c5a1dc457770d86bf49a7
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-113"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
275
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/png
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
melem_close.png
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/
320 B
591 B
66ms
65ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/melem_close.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
db21f6b5d4f3d1ff9270df084c6e8fcbcb7fffa401ab603eb39f1270676b3a84
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-140"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
320
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/png
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
btn_arrow_w.png
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/
307 B
578 B
67ms
65ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/btn_arrow_w.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
12047d9cec7d2c20a364117e5952575290afe090049eff831358cae1e4d2a909
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-133"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
307
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/png
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
breadcrumb_raq.png
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/
179 B
450 B
67ms
66ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/breadcrumb_raq.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
58687cf19f5c4523eb3937b05cb26fb6393d533151ddeea203cdf4c37fadc043
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-b3"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
179
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/png
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
add_to_fav_h.png
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/
420 B
691 B
68ms
66ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/add_to_fav_h.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
1dd6cdb6928c518a0e5e8471f5efba8c8ad2d4219cb9fc1e113845ace1f51ace
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-1a4"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
420
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/png
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
product_desc_point.png
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/
595 B
866 B
64ms
62ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/product_desc_point.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
22822441dbab76d710c8b365045f60825c313ccdbd94c3d5e744b29d64004b99
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-253"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
595
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/png
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
product_avail_1.png
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/
679 B
950 B
64ms
62ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/product_avail_1.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
f5ddabb36e171a9a75696b7260b944c7c5af36f6389ef66e2a25e9422ca6b42e
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-2a7"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
679
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/png
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
product_avail_2.png
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/
593 B
864 B
64ms
63ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/product_avail_2.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
34e8f312f56bdb728fc36d417d6b713c54858713e32bb12a69063ca19d15210c
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-251"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
593
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/png
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
product_avail_3.png
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/
729 B
1000 B
65ms
63ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/product_avail_3.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
28d0dbe614e89adcb3cf3b7df6b6408eb862c831239813107b3493b8b952e78e
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-2d9"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
729
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/png
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
product_avail_4.png
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/
680 B
951 B
71ms
70ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/product_avail_4.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
ab55a1d7e38664843675f1677ae228cd33d8a1224438f1050f8a55a0245dadb1
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-2a8"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
680
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/png
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
btn_basket_w.png
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/
753 B
1 KB
71ms
70ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/btn_basket_w.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
af6057f5b86a3ea981b5c84c060ea7c9daef71c9084038a47eb3bbd807f5831b
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-2f1"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
753
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/png
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
4096-2734-max%20%282%29%20%281%29.jpg
sklep.doppelherz.pl/userdata/public/assets/w%C5%82asne/sgkategorie/
23 KB
23 KB
42ms
41ms
Image
image/jpeg
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/userdata/public/assets/w%C5%82asne/sgkategorie/4096-2734-max%20%282%29%20%281%29.jpg
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
62beacb54fec9c638996da47114fd52e101c451cac6a7ce6dd6b66b410ce7fe1
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"688b550e-5c26"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
23590
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/jpeg
last-modified
Thu, 31 Jul 2025 11:35:42 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
4096-2731-max%20%289%29%20%281%29.jpg
sklep.doppelherz.pl/userdata/public/assets/w%C5%82asne/sgkategorie/
17 KB
17 KB
42ms
42ms
Image
image/jpeg
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/userdata/public/assets/w%C5%82asne/sgkategorie/4096-2731-max%20%289%29%20%281%29.jpg
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
271facec764173c55dbefc01f507d328fe2bde80ca9aa1b909641828dcdc599b
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"688b5326-438b"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
17291
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/jpeg
last-modified
Thu, 31 Jul 2025 11:27:34 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
4096-2731-max%20%2810%29.jpg
sklep.doppelherz.pl/userdata/public/assets/w%C5%82asne/sgkategorie/
15 KB
15 KB
44ms
43ms
Image
image/jpeg
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/userdata/public/assets/w%C5%82asne/sgkategorie/4096-2731-max%20%2810%29.jpg
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
7ba6c4ff950c37c27dcd1a63f7b1b2620baa13048db47f23caaccaf02245ce08
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"688b81fd-3c0f"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
15375
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/jpeg
last-modified
Thu, 31 Jul 2025 14:47:25 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
lemur.d4e14ff3.js Show response
trustmate.io/build/js/widget/
41 KB
12 KB
76ms
75ms
Script
application/javascript
54.192.35.76
Amazon.com
General
Full URL
https://trustmate.io/build/js/widget/lemur.d4e14ff3.js
Requested by
Host: trustmate.io
URL: https://trustmate.io/widget/api/df208cd9-240d-473c-8b8d-16de63da0173/script
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
54.192.35.76 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-54-192-35-76.fra56.r.cloudfront.net
Software
/
Resource Hash
eb1f13a3c5a2db58c3fcf46fb91add8f92fc0687609ee0cb5c5b21f814efe365
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
public, no-transform, max-age=31536000
content-encoding
gzip
etag
W/"6a9a6aa8-a525"
age
1032999
via
1.1 e80e328c1a67b78b31878ecc3bb78c36.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
GHPw8iREXwWE_OS-JSxNpm04H0sr2qH6ckYjy0hQl9U10w-e-xrH-Q==
date
Fri, 04 Sep 2026 07:49:05 GMT
content-type
application/javascript
last-modified
Fri, 04 Sep 2026 06:52:24 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P15
GET
H2
200
hornet.b5289084.js Show response
trustmate.io/build/js/widget/
39 KB
11 KB
77ms
76ms
Script
application/javascript
54.192.35.76
Amazon.com
General
Full URL
https://trustmate.io/build/js/widget/hornet.b5289084.js
Requested by
Host: trustmate.io
URL: https://trustmate.io/widget/api/0acf271b-a747-41cd-84e0-3d83d57d8028/script?product=412
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
54.192.35.76 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-54-192-35-76.fra56.r.cloudfront.net
Software
/
Resource Hash
cbcebbe83e989f5a35dd57e80810bb826b665b4a4006025c5a2675c2cc08b952
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
public, no-transform, max-age=31536000
content-encoding
gzip
etag
W/"6a8e92dd-9cec"
age
1811815
via
1.1 e80e328c1a67b78b31878ecc3bb78c36.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
XYKDQ1ycwD8_iYyOgPaTf0Ym-UeQfyPRfVoe90yWMNukPJ7jH5XY5g==
date
Wed, 26 Aug 2026 07:28:49 GMT
content-type
application/javascript
last-modified
Wed, 26 Aug 2026 07:16:45 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P15
GET
H2
200
hydra.c5dcf127.js Show response
trustmate.io/build/js/widget/
101 KB
25 KB
81ms
70ms
Script
application/javascript
54.192.35.76
Amazon.com
General
Full URL
https://trustmate.io/build/js/widget/hydra.c5dcf127.js
Requested by
Host: trustmate.io
URL: https://trustmate.io/widget/api/1928d3f4-a6ef-4402-a7d7-247ba5e6e1d5/script?product=412
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
54.192.35.76 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-54-192-35-76.fra56.r.cloudfront.net
Software
/
Resource Hash
98f207904c9d527560c3187478b53ace6c1b59f88c2dce829cf04f963377646a
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
public, no-transform, max-age=31536000
content-encoding
gzip
etag
W/"6a9a6aa8-19522"
age
1033012
via
1.1 e80e328c1a67b78b31878ecc3bb78c36.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
tLpQClPh0URFCXzoZ_CMuxSvxhLFZldKhMcUz07vdAC1P7F82qHiMw==
date
Fri, 04 Sep 2026 07:48:52 GMT
content-type
application/javascript
last-modified
Fri, 04 Sep 2026 06:52:24 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P15
GET
H2
200
dodo2.c933ec76.js Show response
trustmate.io/build/js/widget/
21 KB
6 KB
102ms
98ms
Script
application/javascript
54.192.35.76
Amazon.com
General
Full URL
https://trustmate.io/build/js/widget/dodo2.c933ec76.js
Requested by
Host: trustmate.io
URL: https://trustmate.io/widget/api/bc5abbfe-277a-4b98-8b9f-9b8f3509207c/script
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
54.192.35.76 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-54-192-35-76.fra56.r.cloudfront.net
Software
/
Resource Hash
bfca7a4c18c0be53ab27977eb50f79e6f7d6139eb15972ec2cc8963852de9ec0
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
public, no-transform, max-age=31536000
content-encoding
gzip
etag
W/"6a8e92dd-5445"
age
1811812
via
1.1 e80e328c1a67b78b31878ecc3bb78c36.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
kt8EFNGP83ynUSKant2s7feKuHHbzyGCtN25PP-XvGmYegQoonJvYA==
date
Wed, 26 Aug 2026 07:28:52 GMT
content-type
application/javascript
last-modified
Wed, 26 Aug 2026 07:16:45 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P15
GET
H2
200
js Show response
www.googletagmanager.com/gtag/
446 KB
154 KB
125ms
118ms
Script
application/javascript
192.178.183.97
Google LLC
General
Full URL
https://www.googletagmanager.com/gtag/js?id=G-WK4E7DG3RJ&l=dataLayer
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/assets/js/frontstore/main.ab4429d120a166c61eeb.min.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
192.178.183.97 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfraw-in-f97.1e100.net
Software
Google Tag Manager /
Resource Hash
f70f98cd38ad7a9e9faaa25cfbd4bdb9be1a622bfb3f2edb8cc4519d7c286f9d
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
private, max-age=900
content-encoding
zstd
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
expires
Wed, 16 Sep 2026 06:45:44 GMT
access-control-allow-origin
*
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
157829
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
0
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
server
Google Tag Manager
access-control-allow-headers
Cache-Control
GET
H2
200
122.7 Show response
sklep.doppelherz.pl/product/getstockcostinfo/stock/420/price/
729 B
513 B
32ms
31ms
XHR
application/json
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/product/getstockcostinfo/stock/420/price/122.7
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/assets/js/frontstore/main.ab4429d120a166c61eeb.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
20409ae125229780e644e1ca29cfecfdbf283b9e495e343866671222f29d3b83
Security Headers
Name Value
Strict-Transport-Security max-age=60; includeSubdomains
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
X-Requested-With
XMLHttpRequest
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Accept
*/*
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=60; includeSubdomains
content-encoding
gzip
x-content-type-options
nosniff
content-length
308
date
Wed, 16 Sep 2026 06:45:44 GMT
content-type
application/json
x-powered-by
DCSaaS
x-fmc
5
server
DCSaaS/httpd
GET
H2
404
/ Show response
sklep.doppelherz.pl/webapi/front/pl_PL/categories/138/products/PLN/
33 B
297 B
139ms
139ms
XHR
application/json
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/webapi/front/pl_PL/categories/138/products/PLN/?page=1&limit=9
Requested by
Host: dcsaascdn.net
URL: https://dcsaascdn.net/js/front-api-1.5.0.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
8857e1c0419304f0dc9cb82d125512071ed0f44fd4e5b00e228f67fcfb9f1c2e
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-store, no-cache, must-revalidate
content-encoding
gzip
pragma
no-cache
x-content-type-options
nosniff
expires
Thu, 19 Nov 1981 08:52:00 GMT
content-length
53
date
Wed, 16 Sep 2026 06:45:45 GMT
content-type
application/json
x-powered-by
DCSaaS
x-fmc
5
server
DCSaaS/httpd
GET
H2
200
inpostpay.widget.v2.js Show response
inpostpay-widget-v2.inpost.pl/
128 KB
46 KB
133ms
35ms
Script
application/javascript
172.64.146.195
Cloudflare
General
Full URL
https://inpostpay-widget-v2.inpost.pl/inpostpay.widget.v2.js
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/assets/js/frontstore/main.ab4429d120a166c61eeb.min.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.64.146.195 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
f9e0c59e68d5550933488cf67f58f44f0cb5d2a3dd1baabfcf755c46e1d699ed

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
public, max-age=600
content-encoding
gzip
cf-cache-status
HIT
etag
"6a968abc-1fe54"
age
475
via
1.1 google
cf-ray
a3bde8fc8f0bccaf-WAW
expires
Wed, 16 Sep 2026 06:55:45 GMT
server-timing
dtTrId;desc="766798aa7b7b41e25a05d9970fad715f", dtSInfo;desc="1"
alt-svc
h3=":443"; ma=86400
date
Wed, 16 Sep 2026 06:45:45 GMT
content-type
application/javascript; charset=utf-8
last-modified
Tue, 01 Sep 2026 08:20:12 GMT
server
cloudflare
vary
Accept-Encoding
GET
H2
200
delivery_truck.svg
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/
2 KB
3 KB
68ms
68ms
Image
image/svg+xml
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/delivery_truck.svg
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
ec89ee519f3e35a1651bd4081b04502e06f2bf11f6c80122a1cf76c60eab2425
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-985"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
2437
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/svg+xml
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
loader.min.js Show response
cdn.doofinder.com/apps/loader/2.x/
58 KB
21 KB
198ms
77ms
Script
text/javascript
195.181.175.40
CDN77 Datacamp Li...
General
Full URL
https://cdn.doofinder.com/apps/loader/2.x/loader.min.js
Requested by
Host: eu1-config.doofinder.com
URL: https://eu1-config.doofinder.com/2.x/7b75d787-6f54-4376-82da-280ebbba24cf.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
195.181.175.40 Frankfurt am Main, Germany, ASN60068 (CDN77 Datacamp Limited, GB),
Reverse DNS
824291365.fra.cdn77.com
Software
CDN77-Turbo /
Resource Hash
69015d24758dd9d4dbd955d98f36d49e4aa6ee18980fa67fd89f9f60760edf97

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
W/"77b5036b62e1fd2ad66cee24822e7d13"
age
0
x-77-cache
HIT
date
Wed, 16 Sep 2026 06:45:45 GMT
x-rgw-object-type
Normal
content-type
text/javascript; charset=utf-8
last-modified
Tue, 15 Sep 2026 12:49:05 GMT
x-77-nzt-ray
25b0213183f355e63e3baa6ab4ca0208
vary
Accept-Encoding
x-77-nzt
k3Bl499iMoj1for//j7okhO1iwnv0Q/UUCBa9PhD+tnVyA7wZSrruzqpNY8+MfSJSg
cache-control
s-maxage=14400, max-age=120
x-amz-request-id
tx000009a85bb1099642ff5-006aa93ec5-c80c64d-prg
x-77-pop
frankfurtDE
x-77-age
6991
server
CDN77-Turbo
GET
H2
200
cb=gapi.loaded_0 Show response
apis.google.com/_/scs/abc-static/_/js/k=gapi.lb.pl.r2bYKzcHidM.O/m=ratingbadge/rt=j/sv=1/d=1/ed=1/rs=AHpOoo_W5oST4w0nWzAS8ntjYKme90h9Wg/
162 KB
56 KB
50ms
49ms
Script
text/javascript
142.251.14.101
Google LLC
General
Full URL
https://apis.google.com/_/scs/abc-static/_/js/k=gapi.lb.pl.r2bYKzcHidM.O/m=ratingbadge/rt=j/sv=1/d=1/ed=1/rs=AHpOoo_W5oST4w0nWzAS8ntjYKme90h9Wg/cb=gapi.loaded_0?le=scs,fedcm_migration_mod
Requested by
Host: apis.google.com
URL: https://apis.google.com/js/platform.js?onload=renderBadge
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.14.101 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f101.1e100.net
Software
sffe /
Resource Hash
48062ea02ec57d525aaedca180131ae76c4f2ad6fbb6153a37799533daea8a35
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
age
384851
report-to
{"group":"social-frontend-mpm-access","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/social-frontend-mpm-access"}]}
x-content-type-options
nosniff
expires
Sat, 11 Sep 2027 19:51:34 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 11 Sep 2026 19:51:34 GMT
last-modified
Sun, 02 Aug 2026 15:19:54 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
cache-control
public, max-age=31536000
cross-origin-opener-policy
same-origin; report-to="social-frontend-mpm-access"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/social-frontend-mpm-access
accept-ranges
bytes
access-control-allow-origin
*
content-length
56469
x-xss-protection
0
server
sffe
GET
H2
200
Grafika-na-karcie-produktu_lato_1300x400.webp
sklep.doppelherz.pl/userdata/public/assets/w%C5%82asne/karty/bannerykp/
347 KB
348 KB
31ms
31ms
Image
image/webp
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/userdata/public/assets/w%C5%82asne/karty/bannerykp/Grafika-na-karcie-produktu_lato_1300x400.webp
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
a712778c4c78b733915ae9486bf678c2e34fd7f4038262548adbc5680ea13067
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6a4621dc-56d90"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:44 GMT
accept-ranges
bytes
content-length
355728
date
Wed, 16 Sep 2026 06:45:44 GMT
x-xss-protection
1; mode=block
content-type
image/webp
last-modified
Thu, 02 Jul 2026 08:31:24 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
412,421,467,502,513,622,639,658,659 Show response
sklep.doppelherz.pl/webapi/front/pl_PL/products/PLN/list/
162 KB
23 KB
137ms
137ms
XHR
application/json
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/webapi/front/pl_PL/products/PLN/list/412,421,467,502,513,622,639,658,659?page=1&limit=50
Requested by
Host: dcsaascdn.net
URL: https://dcsaascdn.net/js/front-api-1.5.0.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
bb1bdfe0673229d24b730ae82e0897a629997352aa790cbe71194d9e578b3480
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-content-type-options
nosniff
content-length
23492
date
Wed, 16 Sep 2026 06:45:45 GMT
content-type
application/json
x-powered-by
DCSaaS
x-fmc
5
server
DCSaaS/httpd
GET
H2
200
css2
fonts.googleapis.com/
12 KB
1 KB
175ms
74ms
Stylesheet
text/css
142.251.14.95
Google LLC
General
Full URL
https://fonts.googleapis.com/css2?family=Inter:ital,wght@0,400;0,500;0,600;0,700;1,500&display=swap
Requested by
Host:
URL: about:client
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
142.251.14.95 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f95.1e100.net
Software
ESF /
Resource Hash
f29f2543444ecbde565c75bd2f78228b7b2a4adfd0cfbadbd776c4221e32aae3
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-content-type-options
nosniff
expires
Wed, 16 Sep 2026 06:45:45 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 16 Sep 2026 06:45:45 GMT
content-type
text/css; charset=utf-8
vary
Sec-Fetch-Dest, Sec-Fetch-Mode, Sec-Fetch-Site
last-modified
Wed, 16 Sep 2026 06:38:50 GMT
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=31536000
link
<https://fonts.gstatic.com>; rel=preconnect; crossorigin
cache-control
private, max-age=86400, stale-while-revalidate=604800
timing-allow-origin
*
cross-origin-opener-policy
same-origin-allow-popups
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
x-xss-protection
0
server
ESF
GET
H2
200
serduszko_trustmate.png
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/
928 B
1 KB
97ms
96ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/user/serduszko_trustmate.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
43ad90cbb5676957399f2ad5d477d3e480505594ebfe061ab34c84eb55d43d13
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/cache/sfc/NDc6NTM2OjUuMjYuNDg.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-3a0"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:45 GMT
accept-ranges
bytes
content-length
928
date
Wed, 16 Sep 2026 06:45:45 GMT
x-xss-protection
1; mode=block
content-type
image/png
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
DATA
200
OK
truncated
/
3 KB
0
Image
image/svg+xml

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
7b67b770e711d5e0978a15d1cbc18c38b5a2fe524383b3d74017da080937e327

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/svg+xml
GET
DATA
200
OK
truncated
/
1 KB
0
Image
image/svg+xml

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
11a994ac5e338efe9b356fca1cd765e2d946bfab26b8d66c649853d15b8eff4d

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Origin
https://sklep.doppelherz.pl
Referer

Response headers

Content-Type
image/svg+xml
GET
DATA
200
OK
truncated
/
1 KB
0
Image
image/svg+xml

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
e8eabe5ddd83aef657b33998b8b65b469b11cff6cffe0c2e5b18cb1746f071bd

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/svg+xml
GET
DATA
200
OK
truncated
/
354 B
0
Image
image/svg+xml

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
7ce358e16e04aa985cc46d7fe62cc3258ac925db741c20e32156a7909a9acf27

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/svg+xml
GET
DATA
200
OK
truncated
/
1 KB
0
Image
image/svg+xml

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
41a7e41ed792f06f2dcbe5335494d5180251f4050d9420de8e33fa83a17e8311

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Origin
https://sklep.doppelherz.pl
Referer

Response headers

Content-Type
image/svg+xml
GET
DATA
200
OK
truncated
/
1 KB
0
Image
image/svg+xml

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
8855aa7442ff8bc3e1cbc3b394ea694c8211c4ffbba83c699fc27fdbd6cfd734

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Origin
https://sklep.doppelherz.pl
Referer

Response headers

Content-Type
image/svg+xml
GET

trusted.svg
trustmate.io/images/widgets/badges/v2/pl/
0
0


GET
DATA
200
OK
truncated
/
9 KB
9 KB
Image
image/svg+xml

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
21d0ac00a9c583ac821b385bf13653b0156565ba2002ed07f00513469ecf78a4

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/svg+xml
GET
H2
200
trusted.svg
trustmate.io/images/widgets/badges/v2/pl/
29 KB
9 KB
273ms
79ms
Image
image/svg+xml
54.192.35.76
Amazon.com
General
Full URL
https://trustmate.io/images/widgets/badges/v2/pl/trusted.svg
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
54.192.35.76 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-54-192-35-76.fra56.r.cloudfront.net
Software
/
Resource Hash
6c71dcdb721f35868d78d7a81340ba039e36fa599f2edd83154b5ff232f69dd8
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
public, no-transform, max-age=31536000
content-encoding
gzip
etag
W/"6a87ea62-7503"
age
1905265
via
1.1 e80e328c1a67b78b31878ecc3bb78c36.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
oQbYFsToNJQUXUAJp5O9uF6-F0Y8JIVP7i1bpFWjLOcGOsQZ8m7t4w==
date
Tue, 25 Aug 2026 05:31:20 GMT
content-type
image/svg+xml
last-modified
Fri, 21 Aug 2026 06:04:18 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P15
GET
H2
200
popular_3.svg
trustmate.io/images/widgets/badges/v2/pl/
37 KB
13 KB
78ms
75ms
Image
image/svg+xml
54.192.35.76
Amazon.com
General
Full URL
https://trustmate.io/images/widgets/badges/v2/pl/popular_3.svg
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
54.192.35.76 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-54-192-35-76.fra56.r.cloudfront.net
Software
/
Resource Hash
e4e78ee1d2abc8e8d66e574c5a16d1e12e76c4b7a12df0e19435f39300afef48
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
public, no-transform, max-age=31536000
content-encoding
gzip
etag
W/"6a82b41c-92f2"
age
2510204
via
1.1 e80e328c1a67b78b31878ecc3bb78c36.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
4qdqfcxtR86JSSOWjIdght1vycSOOCD36At3T9eooCIDjzcByiJ4ZQ==
date
Tue, 18 Aug 2026 05:29:01 GMT
content-type
image/svg+xml
last-modified
Mon, 17 Aug 2026 07:11:24 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P15
GET
H2
200
helpful.svg
trustmate.io/images/widgets/badges/v2/pl/
53 KB
15 KB
79ms
77ms
Image
image/svg+xml
54.192.35.76
Amazon.com
General
Full URL
https://trustmate.io/images/widgets/badges/v2/pl/helpful.svg
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
54.192.35.76 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-54-192-35-76.fra56.r.cloudfront.net
Software
/
Resource Hash
556fc0fbb171c81ae43b5cffa207a33d18636c7fce9da6b347749f5650007c8b
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
public, no-transform, max-age=31536000
content-encoding
gzip
etag
W/"6a87ea62-d42d"
age
1905286
via
1.1 e80e328c1a67b78b31878ecc3bb78c36.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
_IJRCDFfq2FucoF7RtRGc9zV8eL3BnQZPpMh6ki3gGyUNDo0qovMng==
date
Tue, 25 Aug 2026 05:30:59 GMT
content-type
image/svg+xml
last-modified
Fri, 21 Aug 2026 06:04:18 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P15
GET
H2
200
love_us.svg
trustmate.io/images/widgets/badges/v2/pl/
52 KB
13 KB
80ms
78ms
Image
image/svg+xml
54.192.35.76
Amazon.com
General
Full URL
https://trustmate.io/images/widgets/badges/v2/pl/love_us.svg
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
54.192.35.76 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-54-192-35-76.fra56.r.cloudfront.net
Software
/
Resource Hash
e348cbb735743ddd15c80f083a37f27c65d27d89431617db8021eeb518c78a1d
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
public, no-transform, max-age=31536000
content-encoding
gzip
etag
W/"6a87ea62-d127"
age
2011088
via
1.1 e80e328c1a67b78b31878ecc3bb78c36.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
pcy8RFnY4l2p0UG_JD-QFuddGv5onOtW7PA-JbqkjK6io5mDWGiy5w==
date
Mon, 24 Aug 2026 00:07:37 GMT
content-type
image/svg+xml
last-modified
Fri, 21 Aug 2026 06:04:18 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P15
GET
H2
200
friendly.svg
trustmate.io/images/widgets/badges/v2/pl/
51 KB
14 KB
82ms
81ms
Image
image/svg+xml
54.192.35.76
Amazon.com
General
Full URL
https://trustmate.io/images/widgets/badges/v2/pl/friendly.svg
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
54.192.35.76 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-54-192-35-76.fra56.r.cloudfront.net
Software
/
Resource Hash
72ce74fd5abad46c8c353096014aeb21c25f66bfb03ec1ffbfc91803fa3702c3
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
public, no-transform, max-age=31536000
content-encoding
gzip
etag
W/"6a7db023-ccea"
age
2621091
via
1.1 e80e328c1a67b78b31878ecc3bb78c36.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
DqODqf4zUblAJCj1GUCCQ39N5Dvi8bwuXSs1OguRaRNPeYSgdQFqrQ==
date
Sun, 16 Aug 2026 22:40:54 GMT
content-type
image/svg+xml
last-modified
Thu, 13 Aug 2026 11:53:07 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P15
GET
H2
200
role_model.svg
trustmate.io/images/widgets/badges/v2/pl/
50 KB
15 KB
83ms
82ms
Image
image/svg+xml
54.192.35.76
Amazon.com
General
Full URL
https://trustmate.io/images/widgets/badges/v2/pl/role_model.svg
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
54.192.35.76 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-54-192-35-76.fra56.r.cloudfront.net
Software
/
Resource Hash
acbdf40736c00c1aa4259b69eb015a432f539637cb63f4e4b6a407ddcdf4cf3f
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
public, no-transform, max-age=31536000
content-encoding
gzip
etag
W/"6a8ffb22-c633"
age
1578906
via
1.1 e80e328c1a67b78b31878ecc3bb78c36.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
uNp_7REA0ssrZt5S73pb2OL8YsCGji0jyr58zWXFqERY1M49G_9Vdg==
date
Sat, 29 Aug 2026 00:10:39 GMT
content-type
image/svg+xml
last-modified
Thu, 27 Aug 2026 08:53:54 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P15
GET
H2
200
trendy_1.svg
trustmate.io/images/widgets/badges/v2/pl/
51 KB
14 KB
87ms
85ms
Image
image/svg+xml
54.192.35.76
Amazon.com
General
Full URL
https://trustmate.io/images/widgets/badges/v2/pl/trendy_1.svg
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
54.192.35.76 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-54-192-35-76.fra56.r.cloudfront.net
Software
/
Resource Hash
431179aaa06d94305ca7d88cd4437536c91cc8de41e1e1052b222a8fd4e5aa62
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
public, no-transform, max-age=31536000
content-encoding
gzip
etag
W/"69b3f769-cb67"
age
16084916
via
1.1 e80e328c1a67b78b31878ecc3bb78c36.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
k2sE2nB9QNGqIJNeVeA3OlPysMq0Jr2PlxTxtAp2BZDc2p9eKwC0NQ==
date
Sat, 14 Mar 2026 02:43:49 GMT
content-type
image/svg+xml
last-modified
Fri, 13 Mar 2026 11:39:21 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P15
GET
H2
200
www-player.css
www.youtube.com/s/player/8c3fda2d/ Frame 90C8
531 KB
57 KB
35ms
34ms
Stylesheet
text/css
142.251.156.4
Google LLC
General
Full URL
https://www.youtube.com/s/player/8c3fda2d/www-player.css
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/RIenpVjeLR8?si=BHrZAFVtmPsydAwu
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.156.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
1e6f131e5c23998532caa01dec741cd746efdb7364cffaf33a43f227aaa0d458
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/RIenpVjeLR8?si=BHrZAFVtmPsydAwu
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
71357
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Wed, 15 Sep 2027 10:56:28 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Tue, 15 Sep 2026 10:56:28 GMT
last-modified
Mon, 07 Sep 2026 04:37:27 GMT
content-type
text/css
vary
Accept-Encoding, Origin
cache-control
public, max-age=31536000
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
58390
x-xss-protection
0
server
sffe
GET
H2
200
m=root,base
www.youtube.com/s/_/ytembeds/_/ss/k=ytembeds.base.yhHI5PTSAY8.L.W.O/am=AAAAQA/d=1/br=1/rs=AGKMywFckxIJtzgBgE32myOj2p8_CeQPzg/ Frame 90C8
0
437 B
33ms
32ms
Stylesheet
text/css
142.251.156.4
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/ss/k=ytembeds.base.yhHI5PTSAY8.L.W.O/am=AAAAQA/d=1/br=1/rs=AGKMywFckxIJtzgBgE32myOj2p8_CeQPzg/m=root,base
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/RIenpVjeLR8?si=BHrZAFVtmPsydAwu
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.156.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/RIenpVjeLR8?si=BHrZAFVtmPsydAwu
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

age
64170
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Wed, 15 Sep 2027 12:56:15 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Tue, 15 Sep 2026 12:56:15 GMT
last-modified
Tue, 15 Sep 2026 05:13:46 GMT
content-type
text/css; charset=UTF-8
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
0
x-xss-protection
0
server
sffe
GET
H2
200
m=root,base Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.vgtVVePqX9U.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywF7JRG55jS5G2Q8ZG-NwvA9KK_XTA/ Frame 90C8
456 KB
155 KB
48ms
48ms
Script
text/javascript
142.251.156.4
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.vgtVVePqX9U.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywF7JRG55jS5G2Q8ZG-NwvA9KK_XTA/m=root,base
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/RIenpVjeLR8?si=BHrZAFVtmPsydAwu
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.156.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
36031302e14a6d87552e7dbdb754bf3e977e211e867185b8159f9f15ec5ad235
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/RIenpVjeLR8?si=BHrZAFVtmPsydAwu
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
64167
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Wed, 15 Sep 2027 12:56:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Tue, 15 Sep 2026 12:56:18 GMT
last-modified
Tue, 15 Sep 2026 07:16:21 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
158790
x-xss-protection
0
server
sffe
GET
H2
200
base.js Show response
www.youtube.com/s/player/8c3fda2d/player_embed_es6.vflset/pl_PL/ Frame 90C8
2 MB
473 KB
91ms
90ms
Script
text/javascript
142.251.156.4
Google LLC
General
Full URL
https://www.youtube.com/s/player/8c3fda2d/player_embed_es6.vflset/pl_PL/base.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/RIenpVjeLR8?si=BHrZAFVtmPsydAwu
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.156.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
72431f67caf662916d7e087014a84fc06db938d5ba9abda94c92a2532c7ba125
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/RIenpVjeLR8?si=BHrZAFVtmPsydAwu
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
585388
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Thu, 09 Sep 2027 12:09:17 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 09 Sep 2026 12:09:17 GMT
last-modified
Mon, 07 Sep 2026 04:37:27 GMT
content-type
text/javascript
vary
Accept-Encoding, Origin
cache-control
public, max-age=31536000
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
483870
x-xss-protection
0
server
sffe
GET
H3
200
KFO7CnqEu92Fr1ME7kSn66aGLdTylUAMa3yUBA.woff2
fonts.gstatic.com/s/roboto/v48/ Frame 90C8
39 KB
39 KB
101ms
46ms
Font
font/woff2
192.178.183.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/roboto/v48/KFO7CnqEu92Fr1ME7kSn66aGLdTylUAMa3yUBA.woff2
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/RIenpVjeLR8?si=BHrZAFVtmPsydAwu
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
192.178.183.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfraw-in-f94.1e100.net
Software
sffe /
Resource Hash
20b535fa80c8189e3b87d1803038389960203a886d502bc2ef1857affc2f38d2
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://www.youtube.com
sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

age
397126
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Sat, 11 Sep 2027 16:26:59 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 11 Sep 2026 16:26:59 GMT
last-modified
Thu, 29 May 2025 23:30:55 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
40128
x-xss-protection
0
server
sffe
GET
H2
200
hornet.6a2a46a4.css
trustmate.io/build/css/widget/
44 KB
8 KB
68ms
68ms
Stylesheet
text/css
54.192.35.76
Amazon.com
General
Full URL
https://trustmate.io/build/css/widget/hornet.6a2a46a4.css
Requested by
Host: trustmate.io
URL: https://trustmate.io/widget/api/0acf271b-a747-41cd-84e0-3d83d57d8028/script?product=412
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
54.192.35.76 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-54-192-35-76.fra56.r.cloudfront.net
Software
/
Resource Hash
cbb7c5859592f52cc19c7d9aa0ee7e445d30f8797230915f5ef449ba3799c36e
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
public, no-transform, max-age=31536000
content-encoding
gzip
etag
W/"6aa799ff-af24"
age
168477
via
1.1 e80e328c1a67b78b31878ecc3bb78c36.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
bGP_utnlDwwYgF2nTAouAS8psmShh_pgVK5AKy5CgA3czKiF6B3nbQ==
date
Mon, 14 Sep 2026 07:57:48 GMT
content-type
text/css
last-modified
Mon, 14 Sep 2026 06:53:51 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P15
GET
H2
200
rating-insights.e846280c.js Show response
trustmate.io/build/
33 KB
10 KB
68ms
68ms
Script
application/javascript
54.192.35.76
Amazon.com
General
Full URL
https://trustmate.io/build/rating-insights.e846280c.js
Requested by
Host: trustmate.io
URL: https://trustmate.io/build/js/widget/hornet.b5289084.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
54.192.35.76 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-54-192-35-76.fra56.r.cloudfront.net
Software
/
Resource Hash
dd17587ea74f09a0b739c47f2483899bb38f983bd3f59248a8d825d84ed3a2ff
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
public, no-transform, max-age=31536000
content-encoding
gzip
etag
W/"6a8ffb21-85a3"
age
1578633
via
1.1 e80e328c1a67b78b31878ecc3bb78c36.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
FmqyjN2ecd-y8I_nSelWQFZ8pkcJn6ZFHC6IVDynBLnT-M4oLqcTBA==
date
Sat, 29 Aug 2026 00:15:12 GMT
content-type
application/javascript
last-modified
Thu, 27 Aug 2026 08:53:53 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P15
GET
H2
200
ir.js Show response
pixel.wp.pl/w/WP-ADS-WP-ADS-LN9ZN-JUK/
2 KB
2 KB
30ms
29ms
XHR
application/javascript
212.77.113.26
WirtualnaPolska W...
General
Full URL
https://pixel.wp.pl/w/WP-ADS-WP-ADS-LN9ZN-JUK/ir.js
Requested by
Host: pixel.wp.pl
URL: https://pixel.wp.pl/w/tr.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
212.77.113.26 , Poland, ASN12827 (WirtualnaPolska Wirtualna Polska Media S.A., PL),
Reverse DNS
Software
nginx /
Resource Hash
b93064d21480c5124df876c3c8e61a022f0ef7426c261ba22ec3a0d1fb09365c

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=60, must-revalidate
etag
"6aa929e6-67a"
accept-ch
device-memory, dpr, width, viewport-width, rtt, downlink, ect, sec-ch-ua, sec-ch-ua-platform, sec-ch-ua-mobile, sec-ch-ua-full-version-list, sec-ch-ua-platform-version, sec-ch-ua-arch, sec-ch-ua-bitness, sec-ch-ua-model
access-control-allow-credentials
true
x-op-id-all
1a1r1d
accept-ch-lifetime
604800
accept-ranges
bytes
access-control-allow-origin
https://sklep.doppelherz.pl
content-length
1658
date
Wed, 16 Sep 2026 06:45:45 GMT
content-type
application/javascript
last-modified
Tue, 15 Sep 2026 11:20:06 GMT
server
nginx
GET
H2
200
heart-4.svg
trustmate.io/images/widgets/rating/stars/
1 KB
1 KB
52ms
52ms
Image
image/svg+xml
54.192.35.76
Amazon.com
General
Full URL
https://trustmate.io/images/widgets/rating/stars/heart-4.svg
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
54.192.35.76 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-54-192-35-76.fra56.r.cloudfront.net
Software
/
Resource Hash
236c948683a9914019dd81d7b331e9bd4e90b0adfc8c5d49687e6e086f6aac35
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
public, no-transform, max-age=31536000
content-encoding
gzip
etag
W/"697e16fc-471"
age
19505126
via
1.1 e80e328c1a67b78b31878ecc3bb78c36.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
zJ7hDjIxFRv-iLVLFVxo3SfDhKwkryy46SklXXbwB1CBP5xCJxWTxA==
date
Mon, 02 Feb 2026 12:40:19 GMT
content-type
image/svg+xml
last-modified
Sat, 31 Jan 2026 14:51:40 GMT
vary
Accept-Encoding
x-amz-cf-pop
FRA56-P15
GET
DATA
200
OK
truncated
/
2 KB
0
Image
image/svg+xml

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
2e0ebf9634e3de6550e1c41af6b81954ac148c2f54f821a2b1fb138ead8333c0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Origin
https://sklep.doppelherz.pl
Referer

Response headers

Content-Type
image/svg+xml
GET
DATA
200
OK
truncated
/
2 KB
0
Image
image/svg+xml

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
46093e6d7d2d64f56fade236b081136d4dec25a7ef591576e20183a8238c981f

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Origin
https://sklep.doppelherz.pl
Referer

Response headers

Content-Type
image/svg+xml
GET
DATA
200
OK
truncated
/
237 B
0
Image
image/svg+xml

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
5ea63270f0913583a9b5763305d3b971bacf709d8640055654de563e2286b736

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/svg+xml
GET
DATA
200
OK
truncated
/
1 KB
0
Image
image/svg+xml

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
5b8f987f90f9a084e87e153fd4be8d037362202681f2b17f5bbc0cc60b811541

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Origin
https://sklep.doppelherz.pl
Referer

Response headers

Content-Type
image/svg+xml
GET
DATA
200
OK
truncated
/
354 B
0
Image
image/svg+xml

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
4067f5146e4ae5178fcfd00cae33f20b160da24dbc611ddc2d880b82f8c439f7

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer

Response headers

Content-Type
image/svg+xml
GET
H2
200
120_120_productGfx_1342.webp
sklep.doppelherz.pl/environment/cache/images/
5 KB
5 KB
49ms
48ms
Image
image/webp
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/environment/cache/images/120_120_productGfx_1342.webp
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
3a2d459adec3d78b95511ee25423235aabf6ecf35b24bed5605ec5ecb7c1de29
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000
etag
dfd4e32fa4f1528448bcda1b3fa07980
x-content-type-options
nosniff
accept-ranges
bytes
content-length
4832
date
Wed, 16 Sep 2026 06:45:45 GMT
content-type
image/webp
last-modified
Mon, 17 Aug 2026 18:09:02 GMT
server
DCSaaS/httpd
x-powered-by
DCSaaS
GET
H2
200
120_120_productGfx_1341.webp
sklep.doppelherz.pl/environment/cache/images/
5 KB
5 KB
50ms
48ms
Image
image/webp
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/environment/cache/images/120_120_productGfx_1341.webp
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
a35e321c618cdfcf0ccef374f79e067954985aeb624d4b76f301870dfaab41e0
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000
etag
9c3cd6806919ea5e6d3421a1f747d17c
x-content-type-options
nosniff
accept-ranges
bytes
content-length
4784
date
Wed, 16 Sep 2026 06:45:45 GMT
content-type
image/webp
last-modified
Mon, 17 Aug 2026 18:09:02 GMT
server
DCSaaS/httpd
x-powered-by
DCSaaS
GET
H2
200
120_120_productGfx_1255.webp
sklep.doppelherz.pl/environment/cache/images/
4 KB
4 KB
68ms
67ms
Image
image/webp
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/environment/cache/images/120_120_productGfx_1255.webp
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
2279d34a095ca33040f7f9d86c7de1ff7d2c14a4fdf7f9346c77fa8f2f0d721f
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000
etag
4aaeed61d8f115b603636b92d55f2770
x-content-type-options
nosniff
accept-ranges
bytes
content-length
3992
date
Wed, 16 Sep 2026 06:45:45 GMT
content-type
image/webp
last-modified
Mon, 17 Aug 2026 18:09:02 GMT
server
DCSaaS/httpd
x-powered-by
DCSaaS
GET
H2
200
120_120_productGfx_1268.webp
sklep.doppelherz.pl/environment/cache/images/
3 KB
4 KB
50ms
49ms
Image
image/webp
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/environment/cache/images/120_120_productGfx_1268.webp
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
7cceaf0ca77192d6425528a063348b48a76e41428822f9db1d88e5370f05e6f1
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000
etag
b9db00a3f6dc7d0b65b974a5de1220fa
x-content-type-options
nosniff
accept-ranges
bytes
content-length
3570
date
Wed, 16 Sep 2026 06:45:45 GMT
content-type
image/webp
last-modified
Mon, 17 Aug 2026 18:09:02 GMT
server
DCSaaS/httpd
x-powered-by
DCSaaS
GET
H2
200
120_120_productGfx_513.png
sklep.doppelherz.pl/environment/cache/images/
18 KB
18 KB
51ms
50ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/environment/cache/images/120_120_productGfx_513.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
97fd6fc793cd02667ee46858c161ecdd83e9f530673cf4de696486fb14087b59
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000
etag
7ffdae1f011894de819c68de9697cd67
x-content-type-options
nosniff
accept-ranges
bytes
content-length
18386
date
Wed, 16 Sep 2026 06:45:45 GMT
content-type
image/png
last-modified
Mon, 17 Aug 2026 18:09:02 GMT
server
DCSaaS/httpd
x-powered-by
DCSaaS
GET
H2
200
120_120_productGfx_436.jpg
sklep.doppelherz.pl/environment/cache/images/
5 KB
5 KB
50ms
49ms
Image
image/jpeg
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/environment/cache/images/120_120_productGfx_436.jpg
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
96fb40d39a9c00eb427de8106327259fd0369343343f54210a224094f8806107
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000
etag
847101300afd7a657f36356a1234a303
x-content-type-options
nosniff
accept-ranges
bytes
content-length
5234
date
Wed, 16 Sep 2026 06:45:45 GMT
content-type
image/jpeg
last-modified
Mon, 17 Aug 2026 18:09:02 GMT
server
DCSaaS/httpd
x-powered-by
DCSaaS
GET
H2
200
120_120_productGfx_1369.webp
sklep.doppelherz.pl/environment/cache/images/
4 KB
4 KB
62ms
61ms
Image
image/webp
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/environment/cache/images/120_120_productGfx_1369.webp
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
81cf3e24863d159b577250f05e92374755f0984c0d0ec88b8bf02c080f65dcaa
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000
etag
2ada22b35c60cc441a6effdf5d50b5a8
x-content-type-options
nosniff
accept-ranges
bytes
content-length
4306
date
Wed, 16 Sep 2026 06:45:45 GMT
content-type
image/webp
last-modified
Mon, 17 Aug 2026 18:09:02 GMT
server
DCSaaS/httpd
x-powered-by
DCSaaS
GET
H2
200
120_120_productGfx_1374.webp
sklep.doppelherz.pl/environment/cache/images/
4 KB
4 KB
52ms
51ms
Image
image/webp
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/environment/cache/images/120_120_productGfx_1374.webp
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
2c20e3c8e25f086d2876ad6c1640989c834448f299d2e72e4346a32f67258d1f
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000
etag
8484ea27c5b2ec26dc83b1860975b174
x-content-type-options
nosniff
accept-ranges
bytes
content-length
3986
date
Wed, 16 Sep 2026 06:45:45 GMT
content-type
image/webp
last-modified
Mon, 17 Aug 2026 18:09:02 GMT
server
DCSaaS/httpd
x-powered-by
DCSaaS
GET
H2
200
120_120_productGfx_1199.png
sklep.doppelherz.pl/environment/cache/images/
15 KB
15 KB
50ms
50ms
Image
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/environment/cache/images/120_120_productGfx_1199.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
517a673d22e83eacdb62bef3b37e4d957e6ecd73ba590426da1656213560ec30
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000
etag
0924549560b0cb8e16ff655ca3eb64bb
x-content-type-options
nosniff
accept-ranges
bytes
content-length
15546
date
Wed, 16 Sep 2026 06:45:45 GMT
content-type
image/png
last-modified
Mon, 17 Aug 2026 18:09:02 GMT
server
DCSaaS/httpd
x-powered-by
DCSaaS
GET
DATA
200
OK
truncated
/
2 KB
0
Image
image/svg+xml

General
Full URL
data:truncated
Protocol
DATA
Server
-, , ASN (),
Reverse DNS
Software
/
Resource Hash
4dda8415527f60f66f42c7b9e07277e97b142c3c3b52d553cbb2490fcbfb99a8

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Origin
https://sklep.doppelherz.pl
Referer

Response headers

Content-Type
image/svg+xml
GET
H3
200
UcC73FwrK3iLTeHuS_nVMrMxCp50SjIa1ZL7.woff2
fonts.gstatic.com/s/inter/v20/
47 KB
47 KB
100ms
46ms
Font
font/woff2
192.178.183.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/inter/v20/UcC73FwrK3iLTeHuS_nVMrMxCp50SjIa1ZL7.woff2
Requested by
Host: fonts.googleapis.com
URL: https://fonts.googleapis.com/css2?family=Inter:ital,wght@0,400;0,500;0,600;0,700;1,500&display=swap
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
192.178.183.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfraw-in-f94.1e100.net
Software
sffe /
Resource Hash
3100e775e8616cd2611beecfa23a4263d7037586789b43f035236a2e6fbd4c62
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://sklep.doppelherz.pl
sec-ch-ua-platform
"Linux"
Referer
https://fonts.googleapis.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

age
397785
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Sat, 11 Sep 2027 16:16:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 11 Sep 2026 16:16:00 GMT
last-modified
Tue, 09 Sep 2025 18:33:53 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
48256
x-xss-protection
0
server
sffe
GET
H3
200
UcC73FwrK3iLTeHuS_nVMrMxCp50SjIa25L7SUc.woff2
fonts.gstatic.com/s/inter/v20/
83 KB
83 KB
124ms
71ms
Font
font/woff2
192.178.183.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/inter/v20/UcC73FwrK3iLTeHuS_nVMrMxCp50SjIa25L7SUc.woff2
Requested by
Host: fonts.googleapis.com
URL: https://fonts.googleapis.com/css2?family=Inter:ital,wght@0,400;0,500;0,600;0,700;1,500&display=swap
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
192.178.183.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfraw-in-f94.1e100.net
Software
sffe /
Resource Hash
34b9c504cab7a73e37b746343a449132e56cf7b5481af2cb81dc74dcff25c956
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://sklep.doppelherz.pl
sec-ch-ua-platform
"Linux"
Referer
https://fonts.googleapis.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

age
405213
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Sat, 11 Sep 2027 14:12:12 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 11 Sep 2026 14:12:12 GMT
last-modified
Tue, 09 Sep 2025 18:33:54 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
85068
x-xss-protection
0
server
sffe
GET
H3
200
UcCM3FwrK3iLTcvneQg7Ca725JhhKnNqk4j1ebLhAm8SrXTc69tRipWF.woff2
fonts.gstatic.com/s/inter/v20/
25 KB
25 KB
106ms
54ms
Font
font/woff2
192.178.183.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/inter/v20/UcCM3FwrK3iLTcvneQg7Ca725JhhKnNqk4j1ebLhAm8SrXTc69tRipWF.woff2
Requested by
Host: fonts.googleapis.com
URL: https://fonts.googleapis.com/css2?family=Inter:ital,wght@0,400;0,500;0,600;0,700;1,500&display=swap
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
192.178.183.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfraw-in-f94.1e100.net
Software
sffe /
Resource Hash
ec7b5fad608d36d16f65939bd09e70b4bb81446fa7ee32b345d0c2e4fcd174b7
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://sklep.doppelherz.pl
sec-ch-ua-platform
"Linux"
Referer
https://fonts.googleapis.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

age
395263
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Sat, 11 Sep 2027 16:58:02 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 11 Sep 2026 16:58:02 GMT
last-modified
Tue, 09 Sep 2025 18:37:32 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
25636
x-xss-protection
0
server
sffe
GET
H2
200
5.png
trustmate.io/images/widgets/rating/heart-4/
3 KB
3 KB
74ms
73ms
Image
image/png
54.192.35.76
Amazon.com
General
Full URL
https://trustmate.io/images/widgets/rating/heart-4/5.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
54.192.35.76 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-54-192-35-76.fra56.r.cloudfront.net
Software
/
Resource Hash
9b3827f630e8e34b75102a116bd386178ac1733537367f565f2525357dfd7630
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
public, no-transform, max-age=31536000
etag
"697e16fc-b9b"
age
19505122
via
1.1 e80e328c1a67b78b31878ecc3bb78c36.cloudfront.net (CloudFront)
accept-ranges
bytes
x-cache
Hit from cloudfront
content-length
2971
x-amz-cf-id
gVMuLYGQ_15zUAM9XsFZ02R-qCnJPZwK-dxunb5m3QBPNkUpqeg_ZQ==
date
Mon, 02 Feb 2026 12:40:23 GMT
content-type
image/png
last-modified
Sat, 31 Jan 2026 14:51:40 GMT
x-amz-cf-pop
FRA56-P15
GET
H2
204
collect
pixel.wp.pl/api/
0
583 B
32ms
32ms
Image
text/plain
212.77.113.26
WirtualnaPolska W...
General
Full URL
https://pixel.wp.pl/api/collect?k=WP-ADS-WP-ADS-LN9ZN-JUK&h=sklep.doppelherz.pl&r=&l=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&t=1789541145300&v=7.7.25&wph_a=4066677673.1789541145297&wph_st=3793729808.1789541145297&e=UserCreated&s=1&tz=Europe%2FWarsaw&i=c2d9f166add7bb5355599abd91a7470b44e4b7b9
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
212.77.113.26 , Poland, ASN12827 (WirtualnaPolska Wirtualna Polska Media S.A., PL),
Reverse DNS
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, no-store, must-revalidate
accept-ch
device-memory, dpr, width, viewport-width, rtt, downlink, ect, sec-ch-ua, sec-ch-ua-platform, sec-ch-ua-mobile, sec-ch-ua-full-version-list, sec-ch-ua-platform-version, sec-ch-ua-arch, sec-ch-ua-bitness, sec-ch-ua-model
pragma
no-cache
access-control-allow-credentials
true
access-control-allow-methods
GET
x-server-details
BuVsDk1iRW1JDkViDEfEBTfcR92cDFNzDE0EDT66oEVsBFV6O1nTn9KvjWrJB92EBTNJDENcDTe8S4Y1dtLwdTXaRTNvptUaSHeExtYCStOvDul2D7BzZaOadHhaG4eE
accept-ch-lifetime
604800
expires
Thu, 01 Jan 1970 00:00:00 GMT
x-op-id-all
1a1r1d
access-control-allow-origin
p3p
CP="ALL DSP COR CUR ADM DEV TAI PSA PSD IVA IVD CON TEL OUR SAM IND"
date
Wed, 16 Sep 2026 06:45:45 GMT
server
nginx
GET
H2
204
collect
pixel.wp.pl/api/
0
582 B
59ms
59ms
Image
text/plain
212.77.113.26
WirtualnaPolska W...
General
Full URL
https://pixel.wp.pl/api/collect?e=init&s=1&k=WP-ADS-WP-ADS-LN9ZN-JUK&h=sklep.doppelherz.pl&r=&l=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&t=1789541145301&v=7.7.25&wph_a=4066677673.1789541145297&wph_st=3793729808.1789541145297&tz=Europe%2FWarsaw&imt=&i=e1951a532588b9c37de95039d65b43caf18dfb48
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
212.77.113.26 , Poland, ASN12827 (WirtualnaPolska Wirtualna Polska Media S.A., PL),
Reverse DNS
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, no-store, must-revalidate
accept-ch
device-memory, dpr, width, viewport-width, rtt, downlink, ect, sec-ch-ua, sec-ch-ua-platform, sec-ch-ua-mobile, sec-ch-ua-full-version-list, sec-ch-ua-platform-version, sec-ch-ua-arch, sec-ch-ua-bitness, sec-ch-ua-model
pragma
no-cache
access-control-allow-credentials
true
access-control-allow-methods
GET
x-server-details
BuVsDk1iRW1JDkViDEfEBTfcRW22RTl2BFOiDul6oEVsBFV6O1nTn9KvjWrJB92EDu02Bu61BuI8S4Y1dtLwdTXaRTNvptUaSHeExtYCStOvDul2D7BzZaOadT6aDFO1
accept-ch-lifetime
604800
expires
Thu, 01 Jan 1970 00:00:00 GMT
x-op-id-all
1a1r1d
access-control-allow-origin
p3p
CP="ALL DSP COR CUR ADM DEV TAI PSA PSD IVA IVD CON TEL OUR SAM IND"
date
Wed, 16 Sep 2026 06:45:45 GMT
server
nginx
GET
H2
204
collect
pixel.wp.pl/api/
0
581 B
33ms
33ms
Image
text/plain
212.77.113.26
WirtualnaPolska W...
General
Full URL
https://pixel.wp.pl/api/collect?k=WP-ADS-WP-ADS-LN9ZN-JUK&h=sklep.doppelherz.pl&r=&l=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&t=1789541145302&v=7.7.25&wph_a=4066677673.1789541145297&wph_st=3793729808.1789541145297&e=ViewContent&s=1&tz=Europe%2FWarsaw&c_content_name=View&i=c6ae9653815f0505dca67682e4786e21ff97279b
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
212.77.113.26 , Poland, ASN12827 (WirtualnaPolska Wirtualna Polska Media S.A., PL),
Reverse DNS
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, no-store, must-revalidate
accept-ch
device-memory, dpr, width, viewport-width, rtt, downlink, ect, sec-ch-ua, sec-ch-ua-platform, sec-ch-ua-mobile, sec-ch-ua-full-version-list, sec-ch-ua-platform-version, sec-ch-ua-arch, sec-ch-ua-bitness, sec-ch-ua-model
pragma
no-cache
access-control-allow-credentials
true
access-control-allow-methods
GET
x-server-details
BuVsDk1iRW1JDkViDuf1BTfcD92EDT62BTl2DkV3BFNiB9KFInDXN41YoElCBu6cBuh2Bu6JA4Imp9c5Pk1cDulsdHnCp7ns0abmG7nldTZURFSuDaDlDkc7SzDzSi==
accept-ch-lifetime
604800
expires
Thu, 01 Jan 1970 00:00:00 GMT
x-op-id-all
1a1r1d
access-control-allow-origin
p3p
CP="ALL DSP COR CUR ADM DEV TAI PSA PSD IVA IVD CON TEL OUR SAM IND"
date
Wed, 16 Sep 2026 06:45:45 GMT
server
nginx
GET
H2
204
collect
pixel.wp.pl/api/
0
583 B
34ms
34ms
Image
text/plain
212.77.113.26
WirtualnaPolska W...
General
Full URL
https://pixel.wp.pl/api/collect?k=WP-ADS-WP-ADS-LN9ZN-JUK&h=sklep.doppelherz.pl&r=&l=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&t=1789541145303&v=7.7.25&wph_a=4066677673.1789541145297&wph_st=3793729808.1789541145297&e=ViewContent&s=1&tz=Europe%2FWarsaw&c_content_name=ViewProduct&c_contents=%5B%7B%22id%22%3A%22412%22%2C%22name%22%3A%22Doppelherz%C2%AE%20system%20KOLLAGEN%2011.000%20PLUS%2C%2030%20ampu%C5%82ek%20po%2025ml%20%22%2C%22price%22%3A122.7%2C%22category%22%3A%22Doppelherz%20system%22%2C%22quantity%22%3A1%2C%22in_stock%22%3Atrue%7D%5D&c_item_ids=412&c_content_ids=412&i=6c6cc1f66ae6cc9a10d9eb9c9bf4d9c5f769be03
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
212.77.113.26 , Poland, ASN12827 (WirtualnaPolska Wirtualna Polska Media S.A., PL),
Reverse DNS
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, no-store, must-revalidate
accept-ch
device-memory, dpr, width, viewport-width, rtt, downlink, ect, sec-ch-ua, sec-ch-ua-platform, sec-ch-ua-mobile, sec-ch-ua-full-version-list, sec-ch-ua-platform-version, sec-ch-ua-arch, sec-ch-ua-bitness, sec-ch-ua-model
pragma
no-cache
access-control-allow-credentials
true
access-control-allow-methods
GET
x-server-details
BuVsDk1iRW1JDkViDTf1RTfcB92ERT6JBT6URF06oEVsBFV6O1nTn9KvjWrUduBaDEBaBFV2BHJlGzOvZHfvDTZUBkccGgSb0gDqGaUbS91aRT6aZEpuSFZvxaeapuX=
accept-ch-lifetime
604800
expires
Thu, 01 Jan 1970 00:00:00 GMT
x-op-id-all
1a1r1d
access-control-allow-origin
p3p
CP="ALL DSP COR CUR ADM DEV TAI PSA PSD IVA IVD CON TEL OUR SAM IND"
date
Wed, 16 Sep 2026 06:45:45 GMT
server
nginx
GET
H3
200
id Show response
googleads.g.doubleclick.net/pagead/ Frame 90C8
Redirect Chain
  • https://googleads.g.doubleclick.net/pagead/id
  • https://googleads.g.doubleclick.net/pagead/id?slf_rd=1
100 B
146 B
56ms
56ms
XHR
application/json
142.251.14.156
Google LLC
General
Full URL
https://googleads.g.doubleclick.net/pagead/id?slf_rd=1
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/RIenpVjeLR8?si=BHrZAFVtmPsydAwu
Protocol
H3
Server
142.251.14.156 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f156.1e100.net
Software
cafe /
Resource Hash
b61a97a082469e51d111f4e8e0f7e1e8d7dca01dec46d3ad190095ed440e7bd3
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer
https://www.youtube.com/

Response headers

content-encoding
gzip
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
date
Wed, 16 Sep 2026 06:45:45 GMT
content-type
application/json; charset=UTF-8
content-disposition
attachment; filename="f.txt"
cache-control
no-cache, no-store, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
access-control-allow-origin
https://www.youtube.com
content-length
120
x-xss-protection
0
server
cafe

Redirect headers

x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
date
Wed, 16 Sep 2026 06:45:45 GMT
content-type
text/html; charset=UTF-8
cache-control
no-cache, no-store, must-revalidate
location
https://googleads.g.doubleclick.net/pagead/id?slf_rd=1
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
access-control-allow-origin
https://www.youtube.com
content-length
0
x-xss-protection
0
server
cafe
GET
H2
200
ad_status.js Show response
static.doubleclick.net/instream/ Frame 90C8
29 B
495 B
176ms
73ms
Script
text/javascript
142.251.20.148
Google LLC
General
Full URL
https://static.doubleclick.net/instream/ad_status.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.vgtVVePqX9U.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywF7JRG55jS5G2Q8ZG-NwvA9KK_XTA/m=root,base
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.20.148 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bx-in-f148.1e100.net
Software
sffe /
Resource Hash
eed0dc1fdb5d97ed188ae16fd5e1024a5bb744af47340346be2146300a6c54b9
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

age
533
report-to
{"group":"ads-doubleclick-media","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/ads-doubleclick-media"}]}
x-content-type-options
nosniff
expires
Wed, 16 Sep 2026 06:51:52 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 16 Sep 2026 06:36:52 GMT
last-modified
Thu, 12 Dec 2013 23:40:16 GMT
content-type
text/javascript
cache-control
public, max-age=900
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to="ads-doubleclick-media"
content-length
29
x-xss-protection
0
server
sffe
GET
H3
200
m=r78Drb Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.vgtVVePqX9U.2021.O/ck=ytembeds.base.yhHI5PTSAY8.L.W.O/am=AAAAQA/d=1/exm=base,root/excm=base,root/ed=1/br=1/rs=AGKMywErH1X0xtKwaMHbKvaCjG5cuFf... Frame 90C8
907 KB
219 KB
31ms
31ms
Script
text/javascript
142.251.156.4
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.vgtVVePqX9U.2021.O/ck=ytembeds.base.yhHI5PTSAY8.L.W.O/am=AAAAQA/d=1/exm=base,root/excm=base,root/ed=1/br=1/rs=AGKMywErH1X0xtKwaMHbKvaCjG5cuFfNRw/m=r78Drb
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.vgtVVePqX9U.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywF7JRG55jS5G2Q8ZG-NwvA9KK_XTA/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.156.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
ec1bedf7dcfd4410762c2f576adc210ccadcaa8ca082553bf767e6ad008aba97
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/RIenpVjeLR8?si=BHrZAFVtmPsydAwu
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
64167
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Wed, 15 Sep 2027 12:56:18 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Tue, 15 Sep 2026 12:56:18 GMT
last-modified
Tue, 15 Sep 2026 05:13:46 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
224406
x-xss-protection
0
server
sffe
GET
H3
200
W2672_KEYDVrfRY5QYrOrClGZS7tN6Qj8UZZQ2WNMYI.js Show response
www.google.com/js/th/ Frame 90C8
62 KB
24 KB
78ms
30ms
Script
text/javascript
142.251.157.119
Google LLC
General
Full URL
https://www.google.com/js/th/W2672_KEYDVrfRY5QYrOrClGZS7tN6Qj8UZZQ2WNMYI.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.vgtVVePqX9U.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywF7JRG55jS5G2Q8ZG-NwvA9KK_XTA/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.157.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
5b6ebbdbf28460356b7d1639418aceac2946652eed37a423f1465943658d3182
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
183666
report-to
{"group":"botguard-scs","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/botguard-scs"}]}
x-content-type-options
nosniff
expires
Tue, 14 Sep 2027 03:44:39 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Mon, 14 Sep 2026 03:44:39 GMT
last-modified
Wed, 09 Sep 2026 16:00:00 GMT
content-type
text/javascript
vary
Accept-Encoding
cache-control
public, max-age=31536000
cross-origin-opener-policy
same-origin; report-to="botguard-scs"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/botguard-scs
accept-ranges
bytes
content-length
24457
x-xss-protection
0
server
sffe
GET
H2
200
usersync.html Show response
ssp.wp.pl/ecom/ Frame ED54
365 B
503 B
193ms
97ms
Document
text/html
212.77.113.48
WirtualnaPolska W...
General
Full URL
https://ssp.wp.pl/ecom/usersync.html?consent=1&partner_id=WP-ADS-WP-ADS-LN9ZN-JUK
Requested by
Host: pixel.wp.pl
URL: https://pixel.wp.pl/w/tr.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
212.77.113.48 , Poland, ASN12827 (WirtualnaPolska Wirtualna Polska Media S.A., PL),
Reverse DNS
Software
nginx /
Resource Hash
15bbb20f775d60e73623cbeeb80f97f40d92466d7df84fd517b388e09675e73c

Request headers

Referer
https://sklep.doppelherz.pl/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

access-control-allow-credentials
true
access-control-allow-origin
*
cache-control
max-age=900,stale-while-revalidate=86400
content-encoding
gzip
content-length
265
content-type
text/html; charset=utf-8
date
Wed, 16 Sep 2026 06:45:45 GMT
server
nginx
vary
Origin Accept-Encoding
x-op-id-all
1a2r1d
GET
H3
200
/ Show response
www.google.com/shopping/merchantverse/ Frame 0227
61 KB
10 KB
102ms
80ms
Document
text/html
142.251.157.119
Google LLC
General
Full URL
https://www.google.com/shopping/merchantverse/?usegapi=1&merchant_id=569730759&position=BOTTOM_RIGHT&hl=pl&origin=https%3A%2F%2Fsklep.doppelherz.pl&gsrc=3p&jsh=m%3B%2F_%2Fscs%2Fabc-static%2F_%2Fjs%2Fk%3Dgapi.lb.pl.r2bYKzcHidM.O%2Fd%3D1%2Frs%3DAHpOoo_W5oST4w0nWzAS8ntjYKme90h9Wg%2Fm%3D__features__
Requested by
Host: apis.google.com
URL: https://apis.google.com/_/scs/abc-static/_/js/k=gapi.lb.pl.r2bYKzcHidM.O/m=ratingbadge/rt=j/sv=1/d=1/ed=1/rs=AHpOoo_W5oST4w0nWzAS8ntjYKme90h9Wg/cb=gapi.loaded_0?le=scs,fedcm_migration_mod
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.157.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
8e1eb079ac3c2159726f68156036203499a9b4338796a5c848a2da72bf910df2
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script';report-uri /shopping/merchantverse/_/MerchantVerse/cspreport script-src 'report-sample' 'nonce-nDcnAUlBR9LNMqmz4MvQSg' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /shopping/merchantverse/_/MerchantVerse/cspreport;worker-src 'self' script-src 'unsafe-inline' 'unsafe-eval' blob: data: https://apis.google.com/js/client.js https://apis.google.com/js/api.js https://www.google.com/tools/feedback/chat_load.js https://www.google.com/tools/feedback/help_api.js https://www.google.com/tools/feedback/load.js https://www.google.com/tools/feedback/open.js https://www.google.com/tools/feedback/open_to_help_guide_lazy.js https://www.gstatic.com/feedback/js/ https://www.gstatic.com/feedback/js/help/prod/service/lazy.min.js https://www.gstatic.com/inproduct_help/api/main.min.js https://www.gstatic.com/inproduct_help/chatsupport/chatsupport_button_v2.js https://www.gstatic.com/inproduct_help/service/lazy.min.js https://www.gstatic.com/uservoice/feedback/client/web/live/ https://www.gstatic.com/uservoice/surveys/resources/prod/js/survey/ https://www.gstatic.com/_/mss/boq-shopping-merchant-standards/_/js/k=boq-shopping-merchant-standards.MerchantVerse.pl.0UACnxMfynI.2018.O/ https://apis.google.com/_/scs/abc-static/_/js/;report-uri /shopping/merchantverse/_/MerchantVerse/cspreport/fine-allowlist
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://sklep.doppelherz.pl/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cache-control
no-cache, no-store, max-age=0, must-revalidate
content-encoding
gzip
content-security-policy
require-trusted-types-for 'script';report-uri /shopping/merchantverse/_/MerchantVerse/cspreport script-src 'report-sample' 'nonce-nDcnAUlBR9LNMqmz4MvQSg' 'unsafe-inline';object-src 'none';base-uri 'self';report-uri /shopping/merchantverse/_/MerchantVerse/cspreport;worker-src 'self' script-src 'unsafe-inline' 'unsafe-eval' blob: data: https://apis.google.com/js/client.js https://apis.google.com/js/api.js https://www.google.com/tools/feedback/chat_load.js https://www.google.com/tools/feedback/help_api.js https://www.google.com/tools/feedback/load.js https://www.google.com/tools/feedback/open.js https://www.google.com/tools/feedback/open_to_help_guide_lazy.js https://www.gstatic.com/feedback/js/ https://www.gstatic.com/feedback/js/help/prod/service/lazy.min.js https://www.gstatic.com/inproduct_help/api/main.min.js https://www.gstatic.com/inproduct_help/chatsupport/chatsupport_button_v2.js https://www.gstatic.com/inproduct_help/service/lazy.min.js https://www.gstatic.com/uservoice/feedback/client/web/live/ https://www.gstatic.com/uservoice/surveys/resources/prod/js/survey/ https://www.gstatic.com/_/mss/boq-shopping-merchant-standards/_/js/k=boq-shopping-merchant-standards.MerchantVerse.pl.0UACnxMfynI.2018.O/ https://apis.google.com/_/scs/abc-static/_/js/;report-uri /shopping/merchantverse/_/MerchantVerse/cspreport/fine-allowlist
content-type
text/html; charset=utf-8
cross-origin-opener-policy
same-origin
cross-origin-resource-policy
same-site
date
Wed, 16 Sep 2026 06:45:45 GMT
expires
Mon, 01 Jan 1990 00:00:00 GMT
p3p
CP="This is not a P3P policy! See g.co/p3phelp for more info."
permissions-policy
ch-ua-arch=*, ch-ua-bitness=*, ch-ua-full-version=*, ch-ua-full-version-list=*, ch-ua-model=*, ch-ua-wow64=*, ch-ua-form-factors=*, ch-ua-platform=*, ch-ua-platform-version=*
pragma
no-cache
reporting-endpoints
default="/shopping/merchantverse/_/MerchantVerse/web-reports?context=eJzjUtDikmLw0JBiKJK4wtoExPPPe7J9K_ZlYyvxZWN5688mxMMx89uKq2wCE_ZuuMeoZJmUXxhfnJFfUJCZl66bm1qUnJGYV1JYmpiTWVIJ55elFhWnxhsZGJkZWBqa6BkYxxcYAABzICSg"
server
ESF
vary
Sec-Fetch-Dest, Sec-Fetch-Mode, Sec-Fetch-Site
x-content-type-options
nosniff
x-ua-compatible
IE=edge
x-xss-protection
0
GET

trusted.svg
trustmate.io/images/widgets/badges/v2/pl/
0
0


GET
H2
200
css2
fonts.googleapis.com/ Frame 0227
771 B
960 B
200ms
73ms
Stylesheet
text/css
142.251.14.95
Google LLC
General
Full URL
https://fonts.googleapis.com/css2?family=Google+Symbols&icon_names=top_quality_store&display=block
Requested by
Host: www.google.com
URL: https://www.google.com/shopping/merchantverse/?usegapi=1&merchant_id=569730759&position=BOTTOM_RIGHT&hl=pl&origin=https%3A%2F%2Fsklep.doppelherz.pl&gsrc=3p&jsh=m%3B%2F_%2Fscs%2Fabc-static%2F_%2Fjs%2Fk%3Dgapi.lb.pl.r2bYKzcHidM.O%2Fd%3D1%2Frs%3DAHpOoo_W5oST4w0nWzAS8ntjYKme90h9Wg%2Fm%3D__features__
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
142.251.14.95 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f95.1e100.net
Software
ESF /
Resource Hash
da1d86d98f124bff30527f5e86ba5f770d21a9dd30c71231f52ef5afaaddcbaa
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.google.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-content-type-options
nosniff
expires
Wed, 16 Sep 2026 06:45:45 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 16 Sep 2026 06:45:45 GMT
content-type
text/css; charset=utf-8
vary
Sec-Fetch-Dest, Sec-Fetch-Mode, Sec-Fetch-Site
last-modified
Wed, 16 Sep 2026 06:45:45 GMT
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=31536000
link
<https://fonts.gstatic.com>; rel=preconnect; crossorigin
cache-control
private, max-age=86400, stale-while-revalidate=604800
timing-allow-origin
*
cross-origin-opener-policy
same-origin-allow-popups
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
x-xss-protection
0
server
ESF
GET
H3
200
m=_b Show response
www.gstatic.com/_/mss/boq-shopping-merchant-standards/_/js/k=boq-shopping-merchant-standards.MerchantVerse.pl.0UACnxMfynI.2018.O/d=1/excm=_b/ed=1/dg=0/br=1/wt=2/ujg=1/rs=AGZjOkXk5JN09Gk8Q_7NCzuHWK9... Frame 0227
430 KB
148 KB
40ms
39ms
Script
text/javascript
142.251.157.119
Google LLC
General
Full URL
https://www.gstatic.com/_/mss/boq-shopping-merchant-standards/_/js/k=boq-shopping-merchant-standards.MerchantVerse.pl.0UACnxMfynI.2018.O/d=1/excm=_b/ed=1/dg=0/br=1/wt=2/ujg=1/rs=AGZjOkXk5JN09Gk8Q_7NCzuHWK9UrW8OIw/ee=Pjplud:PoEs9b;QGR0gd:Mlhmy;ScI3Yc:e7Hzgb;YIZmRd:A1yn5d;cEt90b:ws9Tlc;dowIGb:ebZ3mb/dti=1/m=_b
Requested by
Host: www.google.com
URL: https://www.google.com/shopping/merchantverse/?usegapi=1&merchant_id=569730759&position=BOTTOM_RIGHT&hl=pl&origin=https%3A%2F%2Fsklep.doppelherz.pl&gsrc=3p&jsh=m%3B%2F_%2Fscs%2Fabc-static%2F_%2Fjs%2Fk%3Dgapi.lb.pl.r2bYKzcHidM.O%2Fd%3D1%2Frs%3DAHpOoo_W5oST4w0nWzAS8ntjYKme90h9Wg%2Fm%3D__features__
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.157.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
0c491ed20fae0cf6d082339fd5758800109ac0dd8c17667c49543d42363097f7
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/boq-infra/shopping-merchant-standards-boq-js-css-signers
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.google.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
48878
report-to
{"group":"boq-infra/shopping-merchant-standards-boq-js-css-signers","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/boq-infra/shopping-merchant-standards-boq-js-css-signers"}]}
x-content-type-options
nosniff
expires
Wed, 15 Sep 2027 17:11:07 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Tue, 15 Sep 2026 17:11:07 GMT
last-modified
Mon, 14 Sep 2026 11:27:23 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding, Origin
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/boq-infra/shopping-merchant-standards-boq-js-css-signers
cache-control
public, immutable, max-age=31536000
cross-origin-opener-policy
same-origin; report-to="boq-infra/shopping-merchant-standards-boq-js-css-signers"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
151266
x-xss-protection
0
server
sffe
GET
H3
200
m=nmoRmb Show response
www.gstatic.com/_/mss/boq-shopping-merchant-standards/_/js/k=boq-shopping-merchant-standards.MerchantVerse.pl.0UACnxMfynI.2018.O/ck=boq-shopping-merchant-standards.MerchantVerse.MDMkaK1jEhg.L.B1.O/... Frame 0227
335 KB
104 KB
33ms
32ms
Script
text/javascript
142.251.157.119
Google LLC
General
Full URL
https://www.gstatic.com/_/mss/boq-shopping-merchant-standards/_/js/k=boq-shopping-merchant-standards.MerchantVerse.pl.0UACnxMfynI.2018.O/ck=boq-shopping-merchant-standards.MerchantVerse.MDMkaK1jEhg.L.B1.O/d=1/exm=_b/excm=_b/ed=1/br=1/wt=2/ujg=1/rs=AGZjOkVkDzIm79JHH8044LPlV_H2Lyir9Q/ee=Pjplud:PoEs9b;QGR0gd:Mlhmy;ScI3Yc:e7Hzgb;YIZmRd:A1yn5d;cEt90b:ws9Tlc;dowIGb:ebZ3mb/dti=1/m=nmoRmb
Requested by
Host: www.google.com
URL: https://www.google.com/shopping/merchantverse/?usegapi=1&merchant_id=569730759&position=BOTTOM_RIGHT&hl=pl&origin=https%3A%2F%2Fsklep.doppelherz.pl&gsrc=3p&jsh=m%3B%2F_%2Fscs%2Fabc-static%2F_%2Fjs%2Fk%3Dgapi.lb.pl.r2bYKzcHidM.O%2Fd%3D1%2Frs%3DAHpOoo_W5oST4w0nWzAS8ntjYKme90h9Wg%2Fm%3D__features__
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.157.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
2452fedbe55b2a8160ccc7c7490ade42ec4b138fa01054f37b8c160d10892328
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/boq-infra/shopping-merchant-standards-boq-js-css-signers
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.google.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
51004
report-to
{"group":"boq-infra/shopping-merchant-standards-boq-js-css-signers","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/boq-infra/shopping-merchant-standards-boq-js-css-signers"}]}
x-content-type-options
nosniff
expires
Wed, 15 Sep 2027 16:35:41 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Tue, 15 Sep 2026 16:35:41 GMT
last-modified
Fri, 11 Sep 2026 01:46:00 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding, Origin
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/boq-infra/shopping-merchant-standards-boq-js-css-signers
cache-control
public, immutable, max-age=31536000
cross-origin-opener-policy
same-origin; report-to="boq-infra/shopping-merchant-standards-boq-js-css-signers"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
106403
x-xss-protection
0
server
sffe
GET
H3
200
m=cwx9N Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.vgtVVePqX9U.2021.O/ck=ytembeds.base.yhHI5PTSAY8.L.W.O/am=AAAAQA/d=1/exm=base,r78Drb,root/excm=base,root/ed=1/br=1/rs=AGKMywErH1X0xtKwaMHbKvaC... Frame 90C8
66 KB
17 KB
30ms
30ms
Script
text/javascript
142.251.157.119
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.vgtVVePqX9U.2021.O/ck=ytembeds.base.yhHI5PTSAY8.L.W.O/am=AAAAQA/d=1/exm=base,r78Drb,root/excm=base,root/ed=1/br=1/rs=AGKMywErH1X0xtKwaMHbKvaCjG5cuFfNRw/m=cwx9N
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.vgtVVePqX9U.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywF7JRG55jS5G2Q8ZG-NwvA9KK_XTA/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.157.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
5f79436bc01391d1fca66a02f7fc3e3a49cb72e3e542932df985b30a3d706c67
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/RIenpVjeLR8?si=BHrZAFVtmPsydAwu
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
64173
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Wed, 15 Sep 2027 12:56:12 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Tue, 15 Sep 2026 12:56:12 GMT
last-modified
Tue, 15 Sep 2026 05:13:46 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
17747
x-xss-protection
0
server
sffe
GET
H2
200
wpjslib-gosync.js Show response
std.wpcdn.pl/wpjslib6/ Frame ED54
96 KB
32 KB
162ms
60ms
Script
text/javascript
212.77.98.32
WirtualnaPolska W...
General
Full URL
https://std.wpcdn.pl/wpjslib6/wpjslib-gosync.js
Requested by
Host: ssp.wp.pl
URL: https://ssp.wp.pl/ecom/usersync.html?consent=1&partner_id=WP-ADS-WP-ADS-LN9ZN-JUK
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
212.77.98.32 Gdansk, Poland, ASN12827 (WirtualnaPolska Wirtualna Polska Media S.A., PL),
Reverse DNS
wpcdn.pl
Software
nginx /
Resource Hash
3a78587186ec7377a4706df9236b46dde257c3a17f0856b19c59d16e6ded76ea

Request headers

Origin
https://ssp.wp.pl
sec-ch-ua-platform
"Linux"
Referer
https://ssp.wp.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

access-control-allow-headers
*
access-control-max-age
900
cache-control
max-age=900, stale-while-revalidate=21600
timing-allow-origin
*
content-encoding
br
etag
W/"84b3d6d13c1cf2f5d1588689034ed2d2"
access-control-allow-methods
GET
access-control-allow-origin
*
date
Wed, 16 Sep 2026 06:45:45 GMT
x-rgw-object-type
Normal
content-type
text/javascript
last-modified
Tue, 15 Sep 2026 14:14:02 GMT
server
nginx
vary
Origin, Accept-Encoding
GET
H2
200
maxresdefault.jpg
i.ytimg.com/vi/RIenpVjeLR8/ Frame 90C8
166 KB
166 KB
273ms
139ms
Image
image/jpeg
142.251.110.119
Google LLC
General
Full URL
https://i.ytimg.com/vi/RIenpVjeLR8/maxresdefault.jpg?sqp=-oaymwEmCIAKENAF8quKqQMa8AEB-AH-CYAC0AWKAgwIABABGGMgYyhjMA8=&rs=AOn4CLCC2g_yvBWp2TlEoAIddgnBuTU22g
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/RIenpVjeLR8?si=BHrZAFVtmPsydAwu
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.110.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f119.1e100.net
Software
sffe /
Resource Hash
add143c285a6823f0ee462bdb906d94912ea79747fb872d1c7779d76a9f36032
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

etag
"0"
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Wed, 16 Sep 2026 08:45:45 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 16 Sep 2026 06:45:45 GMT
content-type
image/jpeg
cache-control
public, max-age=7200
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
169477
x-xss-protection
0
server
sffe
POST
H2
204
collect
region1.google-analytics.com/g/
0
0
161ms
56ms
Fetch
text/plain
216.239.32.36
Google LLC
General
Full URL
https://region1.google-analytics.com/g/collect?v=2&tid=G-WK4E7DG3RJ&gtm=45je69f0h2v9185103690za200zd9185103690&_p=1789541144744&gcs=G100&gcd=13p3p3p2p5l1&npa=1&dma_cps=-&dma=1&cid=904344215.1789541146&frm=0&ngs=1&pscdl=denied&rcb=15&sr=1600x1200&uaa=x86&uab=64&uafvl=Chromium%3B153.0.8010.36%7CGoogle%2520Chrome%3B153.0.8010.36%7CNot_A%2520Brand%3B8.0.0.0&uam=&uamb=0&uap=Linux&uapv=&uaw=0&ul=pl-pl&_s=1&tag_exp=115616985~115938465~115938469~118897920~118897930~120213116~120385423~120469145~120469153&sid=1789541145&sct=1&seg=0&dl=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&dt=Doppelherz%20system%20Kollagen%2011.000%20PLUS%20%7C%2030%20ampu%C5%82ek%20-%20sklep%20Doppelherz&en=page_view&_fv=1&_nsi=1&_ss=1&_ee=1&tfd=1754
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtag/js?id=G-WK4E7DG3RJ&l=dataLayer
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
216.239.32.36 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
Golfe2 /
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, no-store, must-revalidate
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
content-security-policy-report-only
script-src 'none'; form-action 'none'; frame-src 'none'; report-uri https://csp.withgoogle.com/csp/scaffolding/ascnsrsggc:139:0
report-to
{"group":"ascnsrsggc:139:0","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/scaffolding/ascnsrsggc:139:0"}],}
expires
Fri, 01 Jan 1990 00:00:00 GMT
access-control-allow-origin
https://sklep.doppelherz.pl
cross-origin-opener-policy-report-only
same-origin; report-to=ascnsrsggc:139:0
content-length
0
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 16 Sep 2026 06:45:45 GMT
content-type
text/plain
server
Golfe2
GET
H3
200
lazy.min.js Show response
www.gstatic.com/feedback/js/help/prod/service/ Frame 0227
126 KB
40 KB
31ms
31ms
Script
text/javascript
142.251.157.119
Google LLC
General
Full URL
https://www.gstatic.com/feedback/js/help/prod/service/lazy.min.js
Requested by
Host: www.gstatic.com
URL: https://www.gstatic.com/_/mss/boq-shopping-merchant-standards/_/js/k=boq-shopping-merchant-standards.MerchantVerse.pl.0UACnxMfynI.2018.O/d=1/excm=_b/ed=1/dg=0/br=1/wt=2/ujg=1/rs=AGZjOkXk5JN09Gk8Q_7NCzuHWK9UrW8OIw/ee=Pjplud:PoEs9b;QGR0gd:Mlhmy;ScI3Yc:e7Hzgb;YIZmRd:A1yn5d;cEt90b:ws9Tlc;dowIGb:ebZ3mb/dti=1/m=_b
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.157.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
cee6bfcde9890d4b56c653d637bc81ac31dd7007a96bf60e610bc900202c36fc
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.google.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
age
2499
report-to
{"group":"product-feedback-gathering","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/product-feedback-gathering"}]}
x-content-type-options
nosniff
expires
Wed, 16 Sep 2026 06:54:06 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 16 Sep 2026 06:04:06 GMT
last-modified
Tue, 15 Sep 2026 17:52:53 GMT
content-type
text/javascript
vary
Accept-Encoding, Origin
cache-control
public, max-age=3000
cross-origin-opener-policy
same-origin-allow-popups; report-to="product-feedback-gathering"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/product-feedback-gathering
accept-ranges
bytes
content-length
40452
x-xss-protection
0
server
sffe
GET
H2
200
api.js Show response
apis.google.com/js/ Frame 0227
14 KB
6 KB
200ms
73ms
Script
text/javascript
142.251.14.113
Google LLC
General
Full URL
https://apis.google.com/js/api.js
Requested by
Host: www.gstatic.com
URL: https://www.gstatic.com/_/mss/boq-shopping-merchant-standards/_/js/k=boq-shopping-merchant-standards.MerchantVerse.pl.0UACnxMfynI.2018.O/d=1/excm=_b/ed=1/dg=0/br=1/wt=2/ujg=1/rs=AGZjOkXk5JN09Gk8Q_7NCzuHWK9UrW8OIw/ee=Pjplud:PoEs9b;QGR0gd:Mlhmy;ScI3Yc:e7Hzgb;YIZmRd:A1yn5d;cEt90b:ws9Tlc;dowIGb:ebZ3mb/dti=1/m=_b
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.14.113 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f113.1e100.net
Software
sffe /
Resource Hash
e42a5930d9cacbe10862c1f2220e2af95ecbb90abce186ac4797459e3e7cde78
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/gapi-team
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.google.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
"d208175e9d5d109a"
report-to
{"group":"gapi-team","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/gapi-team"}]}
x-content-type-options
nosniff
expires
Wed, 16 Sep 2026 06:45:46 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 16 Sep 2026 06:45:46 GMT
content-type
text/javascript
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/gapi-team
cache-control
private, max-age=1800, stale-while-revalidate=1800
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="gapi-team"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
content-length
5865
x-xss-protection
0
server
sffe
GET
H3
200
4Ua_rENHsxJlGDuGo1OIlJfC6l_24rlCK1Yo_Iqcsih3SAyH6cAwhX9RFD48TE63OOYKtrwEIJllpyk.woff2
fonts.gstatic.com/s/googlesans/v62/ Frame 0227
22 KB
22 KB
48ms
48ms
Font
font/woff2
192.178.183.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/googlesans/v62/4Ua_rENHsxJlGDuGo1OIlJfC6l_24rlCK1Yo_Iqcsih3SAyH6cAwhX9RFD48TE63OOYKtrwEIJllpyk.woff2
Requested by
Host: www.google.com
URL: https://www.google.com/shopping/merchantverse/?usegapi=1&merchant_id=569730759&position=BOTTOM_RIGHT&hl=pl&origin=https%3A%2F%2Fsklep.doppelherz.pl&gsrc=3p&jsh=m%3B%2F_%2Fscs%2Fabc-static%2F_%2Fjs%2Fk%3Dgapi.lb.pl.r2bYKzcHidM.O%2Fd%3D1%2Frs%3DAHpOoo_W5oST4w0nWzAS8ntjYKme90h9Wg%2Fm%3D__features__
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
192.178.183.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfraw-in-f94.1e100.net
Software
sffe /
Resource Hash
58180e3cba5a736e1875c690b3a756dabc7ee19960f4c66a692d42e5679c13d0
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://www.google.com
sec-ch-ua-platform
"Linux"
Referer
https://www.google.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

age
395899
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Sat, 11 Sep 2027 16:47:26 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 11 Sep 2026 16:47:26 GMT
last-modified
Tue, 29 Oct 2024 18:38:00 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
22180
x-xss-protection
0
server
sffe
POST
H3
200
batchexecute Show response
www.google.com/shopping/merchantverse/_/MerchantVerse/data/ Frame 0227
221 B
234 B
110ms
109ms
XHR
application/json
142.251.157.119
Google LLC
General
Full URL
https://www.google.com/shopping/merchantverse/_/MerchantVerse/data/batchexecute?rpcids=BDBdAd&source-path=%2Fshopping%2Fmerchantverse%2F&bl=boq_shopping-merchantquality-merchantverse_20260914.03_p0&f.sid=-504047560818085674&hl=pl&_reqid=31546&rt=c
Requested by
Host: www.gstatic.com
URL: https://www.gstatic.com/_/mss/boq-shopping-merchant-standards/_/js/k=boq-shopping-merchant-standards.MerchantVerse.pl.0UACnxMfynI.2018.O/d=1/excm=_b/ed=1/dg=0/br=1/wt=2/ujg=1/rs=AGZjOkXk5JN09Gk8Q_7NCzuHWK9UrW8OIw/ee=Pjplud:PoEs9b;QGR0gd:Mlhmy;ScI3Yc:e7Hzgb;YIZmRd:A1yn5d;cEt90b:ws9Tlc;dowIGb:ebZ3mb/dti=1/m=_b
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.157.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
b4c61947bb1a0bf46137576db451d1893e11058d98f591c676d96be5b4d1276d
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script';report-uri /shopping/merchantverse/_/MerchantVerse/cspreport
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.google.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
application/x-www-form-urlencoded;charset=UTF-8
sec-ch-ua-mobile
?0
X-Same-Domain
1

Response headers

content-encoding
gzip
x-content-type-options
nosniff
expires
Mon, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
CP="This is not a P3P policy! See g.co/p3phelp for more info."
date
Wed, 16 Sep 2026 06:45:45 GMT
content-type
application/json; charset=utf-8
vary
Sec-Fetch-Dest, Sec-Fetch-Mode, Sec-Fetch-Site
content-disposition
attachment; filename="response.bin"; filename*=UTF-8''response.bin
x-frame-options
SAMEORIGIN
content-security-policy
require-trusted-types-for 'script';report-uri /shopping/merchantverse/_/MerchantVerse/cspreport
cache-control
no-cache, no-store, max-age=0, must-revalidate
cross-origin-opener-policy
same-origin
pragma
no-cache
accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
cross-origin-resource-policy
same-site
permissions-policy
ch-ua-arch=*, ch-ua-bitness=*, ch-ua-full-version=*, ch-ua-full-version-list=*, ch-ua-model=*, ch-ua-wow64=*, ch-ua-form-factors=*, ch-ua-platform=*, ch-ua-platform-version=*
x-xss-protection
0
server
ESF
GET
H3
204
generate_204
www.youtube.com/ Frame 90C8
0
10 B
30ms
30ms
Image
text/plain
142.251.157.119
Google LLC
General
Full URL
https://www.youtube.com/generate_204?BeTtag
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/RIenpVjeLR8?si=BHrZAFVtmPsydAwu
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.157.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/RIenpVjeLR8?si=BHrZAFVtmPsydAwu
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
0
date
Wed, 16 Sep 2026 06:45:45 GMT
cross-origin-resource-policy
cross-origin
GET
H2
200
getuid Show response
ssp.wp.pl/v1/sync/ Frame ED54
66 B
343 B
32ms
32ms
Fetch
text/plain
212.77.113.48
WirtualnaPolska W...
General
Full URL
https://ssp.wp.pl/v1/sync/getuid
Requested by
Host: std.wpcdn.pl
URL: https://std.wpcdn.pl/wpjslib6/wpjslib-gosync.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
212.77.113.48 , Poland, ASN12827 (WirtualnaPolska Wirtualna Polska Media S.A., PL),
Reverse DNS
Software
nginx /
Resource Hash
824e85572e5cf8dee8943f85e6938b69b2ddd5bc34b807b12dd503ae9ac23532

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://ssp.wp.pl/ecom/usersync.html?consent=1&partner_id=WP-ADS-WP-ADS-LN9ZN-JUK
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

access-control-allow-credentials
true
x-op-id-all
1a2r1d
access-control-allow-origin
*
content-length
66
date
Wed, 16 Sep 2026 06:45:45 GMT
content-type
text/plain; charset=utf-8
vary
Origin
server
nginx
GET
H2
200
js Show response
www.googletagmanager.com/gtag/
579 KB
189 KB
73ms
73ms
Script
application/javascript
192.178.183.97
Google LLC
General
Full URL
https://www.googletagmanager.com/gtag/js?id=G-03LP30MEMG&cx=c&gtm=4e69e1
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtm.js?id=GTM-MBRKD4N
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
192.178.183.97 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfraw-in-f97.1e100.net
Software
Google Tag Manager /
Resource Hash
6cbd3b98bf49873d5137daa50e8074a5b3071ff63e8915a8b34174c4d9feb96e
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
private, max-age=900
content-encoding
zstd
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
expires
Wed, 16 Sep 2026 06:45:45 GMT
access-control-allow-origin
*
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
193390
date
Wed, 16 Sep 2026 06:45:45 GMT
x-xss-protection
0
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
server
Google Tag Manager
access-control-allow-headers
Cache-Control
GET
H2
200
js Show response
www.googletagmanager.com/gtag/
554 KB
182 KB
82ms
82ms
Script
application/javascript
192.178.183.97
Google LLC
General
Full URL
https://www.googletagmanager.com/gtag/js?id=G-Y3J94C59MN&cx=c&gtm=4e69e1
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtm.js?id=GTM-MBRKD4N
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
192.178.183.97 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfraw-in-f97.1e100.net
Software
Google Tag Manager /
Resource Hash
a8b7c779dec08a89faec495f6c654f263edc35b4fa24f22fe2dc9e1de722a6b2
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
private, max-age=900
content-encoding
zstd
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
expires
Wed, 16 Sep 2026 06:45:46 GMT
access-control-allow-origin
*
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
186154
date
Wed, 16 Sep 2026 06:45:46 GMT
x-xss-protection
0
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
server
Google Tag Manager
access-control-allow-headers
Cache-Control
GET
H2
200
js Show response
www.googletagmanager.com/gtag/
420 KB
148 KB
103ms
103ms
Script
application/javascript
192.178.183.97
Google LLC
General
Full URL
https://www.googletagmanager.com/gtag/js?id=G-00000000&cx=c&gtm=4e69e1
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtm.js?id=GTM-MBRKD4N
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
192.178.183.97 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfraw-in-f97.1e100.net
Software
Google Tag Manager /
Resource Hash
d5c9a3a2c47304fe98c43aa058e13eedb8202b7e317bc56f32dbda493bab2c5c
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
private, max-age=900
content-encoding
zstd
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
expires
Wed, 16 Sep 2026 06:45:46 GMT
access-control-allow-origin
*
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
150971
date
Wed, 16 Sep 2026 06:45:46 GMT
x-xss-protection
0
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
server
Google Tag Manager
access-control-allow-headers
Cache-Control
GET
H2
200
118697.js Show response
www.dwin1.com/
65 KB
18 KB
246ms
103ms
Script
application/javascript
54.192.35.44
Amazon.com
General
Full URL
https://www.dwin1.com/118697.js
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtm.js?id=GTM-MBRKD4N
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
54.192.35.44 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-54-192-35-44.fra56.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
1382786d10045c02d2ba5d7a2569045b6fd5f41fd6c2db17325897646b78473d

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-amz-version-id
ZPirlkTOA5XhyplqD38bJHjZ8Im17j2h
etag
W/"48497f85524ee8382316dce9a0d55504"
age
246
access-control-allow-methods
GET, HEAD
x-cache
Hit from cloudfront
x-amz-cf-id
yLRBGAZy4_FvPlkWmxwqncaCZWumJoPIQBKTGxKfd0TAoy7O7nPTCg==
date
Wed, 16 Sep 2026 06:41:52 GMT
content-type
application/javascript; charset=utf-8
vary
Accept-Encoding
last-modified
Tue, 01 Sep 2026 06:27:44 GMT
x-amz-replication-status
COMPLETED
cache-control
max-age=600, s-maxage=600
via
1.1 bdc2f66522ff252ddfe00f314b451db4.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-amz-cf-pop
FRA56-P15
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H2
200
/ Show response
smct.co/tm/
19 KB
6 KB
325ms
136ms
Script
application/javascript
46.137.100.189
Amazon.com
General
Full URL
https://smct.co/tm/?t=sklep.doppelherz.pl
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtm.js?id=GTM-MBRKD4N
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
46.137.100.189 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-46-137-100-189.eu-west-1.compute.amazonaws.com
Software
Apache/2.4.62 (Ubuntu) /
Resource Hash
48914f8d390cea31360e88a9fe8af32fa81f1e81dee479838247d253333f2df9

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=120, must-revalidate
content-encoding
gzip
pragma
cache
etag
"78fc7fb7758d3e6607a020cccb81d303-gzip"
expires
Wed, 16 Sep 2026 06:47:46 GMT
content-length
6246
date
Wed, 16 Sep 2026 06:45:46 GMT
content-type
application/javascript; charset=utf-8
vary
Accept-Encoding
server
Apache/2.4.62 (Ubuntu)
GET
H2
200
trackpoint-async.js Show response
s2.adform.net/banners/scripts/st/
81 KB
31 KB
297ms
109ms
Script
text/javascript
37.157.4.21
ADFORM Adform A/S
General
Full URL
https://s2.adform.net/banners/scripts/st/trackpoint-async.js
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
37.157.4.21 , Denmark, ASN198622 (ADFORM Adform A/S, DK),
Reverse DNS
Software
nginx /
Resource Hash
59938868870ce60b8576506d0211346d8a85329a9d54997c39d921389c493b34

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-cache-status
HIT
cache-control
public, max-age=604800
content-encoding
gzip
etag
W/"cbd67ec72136561be113efd03055f4f4"
access-control-allow-origin
*
date
Wed, 16 Sep 2026 06:45:46 GMT
content-type
text/javascript
vary
Accept-Encoding
server
nginx
last-modified
Tue, 01 Sep 2026 12:25:41 GMT
GET
H2
200
matomo.js Show response
analytics.queisser.com/
82 KB
25 KB
259ms
92ms
Script
application/javascript
142.132.237.132
HETZNER-AS Hetzne...
General
Full URL
https://analytics.queisser.com/matomo.js
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.132.237.132 Falkenstein, Germany, ASN24940 (HETZNER-AS Hetzner Online GmbH, DE),
Reverse DNS
static.132.237.132.142.clients.your-server.de
Software
nginx /
Resource Hash
effd4299323311672d4b36d1cf9e80442531d96c440f9a2bd7c0294dbb34a458

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=3600, public
content-encoding
br
etag
W/"6a047620-146d5"
pragma
public
expires
Wed, 16 Sep 2026 07:45:46 GMT
date
Wed, 16 Sep 2026 06:45:46 GMT
content-type
application/javascript
last-modified
Wed, 13 May 2026 13:01:20 GMT
server
nginx
vary
Accept-Encoding
GET
H3
200
trackpoint.min.js Show response
sites.adquery.io/js/
7 KB
3 KB
77ms
35ms
Script
application/javascript
104.26.0.138
Cloudflare
General
Full URL
https://sites.adquery.io/js/trackpoint.min.js
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.26.0.138 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
b70fd1f6f3b7cfa655772cc3a20eb9e74e85d5f2c7f6d9ce2cd645e9f39ab82a
Security Headers
Name Value
Strict-Transport-Security max-age=7776000

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
1000
content-encoding
zstd
cf-cache-status
HIT
etag
W/"6aa95067-1aaf"
age
3789
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=MG%2BsmRqgdI8OcHugEWRY3bnthC1ThgqoY8KkCxneUDI063AmbwI4Tnzrln77u5lXZ0NEwdqK6hQSqo4YQGLpT6WA7eewsLR6ENCr0%2BGxd8dT4hECA9Z42NEl0yJOMTsiD%2FuE"}]}
access-control-allow-methods
POST, GET, OPTIONS, DELETE, PUT
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Wed, 16 Sep 2026 06:45:46 GMT
content-type
application/javascript
last-modified
Tue, 15 Sep 2026 14:04:23 GMT
priority
u=3,i=?0
access-control-allow-headers
x-requested-with, Content-Type, origin, authorization, accept, client-security-token
strict-transport-security
max-age=7776000
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
cache-control
max-age=14400
cf-ray
a3bde902ad317fba-WAW
access-control-allow-origin
*
server
cloudflare
GET
H/1.1
200
OK
p75395u.js Show response
dfd.doppelherz.pl/u/37/
7 B
697 B
269ms
126ms
Fetch
application/javascript
95.131.136.1
CLARANET-AS Clara...
General
Full URL
https://dfd.doppelherz.pl/u/37/p75395u.js
Requested by
Host: dfd.doppelherz.pl
URL: https://dfd.doppelherz.pl/js/na/na/u/4d647c7fbb.js
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_256_GCM
Server
95.131.136.1 , France, ASN8426 (CLARANET-AS Claranet Limited, GB),
Reverse DNS
front.netaffiliation.net
Software
nginx /
Resource Hash
05b557d5989e0977ad7d6bee47698a1b0582a6dbe6b7e2e1ebb04fb95b54ea2d
Security Headers
Name Value
Strict-Transport-Security max-age=63072000

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

Transfer-Encoding
chunked
Strict-Transport-Security
max-age=63072000
Cache-Control
private, max-age=3600
Content-Encoding
gzip
Connection
keep-alive
Access-Control-Allow-Credentials
true
Referrer-Policy
origin-when-cross-origin
Access-Control-Allow-Origin
https://sklep.doppelherz.pl
Date
Wed, 16 Sep 2026 06:45:46 GMT
Content-Type
application/javascript
Vary
Accept-Encoding, Origin
Server
nginx
Access-Control-Allow-Headers
DNT,X-CustomHeader,Keep-Alive,User-Agent,X-Requested-With,If-Modified-Since,Cache-Control,Content-Type,X-Kwanko-Content-Type,X-Kwanko-Sdk-Version,X-KWKunijs-Debug,X-KWKunijs-Version
POST
H3
200
collect
pagead2.googlesyndication.com/ccm/
0
0
111ms
56ms
Fetch
text/plain
142.251.20.156
Google LLC
General
Full URL
https://pagead2.googlesyndication.com/ccm/collect?rcb=11&frm=0&apvc=1&ae=g&en=page_view&dl=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&scrsrc=www.googletagmanager.com&rnd=704081011.1789541146&navt=n&npa=1&ep.ads_data_redaction=0&_tu=CA&gtm=45He69e1v865320812za200zd865320812xeaxf1&gcs=G100&gcd=13q3q3q2q5l1&dma_cps=-&dma=1&tag_exp=115616985~115938465~115938468~118897920~118897930~120385423~120469145~120469153~120912439&tft=1789541145975&tfd=1946&fmt=8
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtm.js?id=GTM-MBRKD4N
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.20.156 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bx-in-f156.1e100.net
Software
/
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

OPTIONS
H2
200
GenerateIT
jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/ Frame
0
0
163ms
59ms
Preflight
text/html
172.217.116.4
Google LLC
General
Full URL
https://jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/GenerateIT
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
172.217.116.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

Accept
*/*
Access-Control-Request-Headers
content-type,x-goog-api-key
Access-Control-Request-Method
POST
Origin
https://www.youtube.com
Sec-Fetch-Mode
cors
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36

Response headers

access-control-allow-credentials
true
access-control-allow-headers
content-type,x-goog-api-key
access-control-allow-methods
DELETE,GET,HEAD,OPTIONS,PATCH,POST,PUT
access-control-allow-origin
https://www.youtube.com
access-control-max-age
3600
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
0
content-type
text/html
date
Wed, 16 Sep 2026 06:45:46 GMT
server
ESF
vary
origin referer x-origin
x-content-type-options
nosniff
x-frame-options
SAMEORIGIN
x-xss-protection
0
POST
H2
200
GenerateIT Show response
jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/ Frame 90C8
94 B
304 B
54ms
53ms
XHR
application/json+protobuf
172.217.116.4
Google LLC
General
Full URL
https://jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/GenerateIT
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.vgtVVePqX9U.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywF7JRG55jS5G2Q8ZG-NwvA9KK_XTA/m=root,base
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
172.217.116.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
c3d856cc20c7b6a77ee63d0577f3ad804126fe8b58999496781e8b94cc4ca335
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

X-Goog-Api-Key
AIzaSyDyT5W0Jh49F30Pqqtyfdf7pDLFKLJoAnw
sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
application/json+protobuf
sec-ch-ua-mobile
?0

Response headers

access-control-expose-headers
vary,vary,vary,content-encoding,date,server,content-length
content-encoding
gzip
access-control-allow-credentials
true
x-content-type-options
nosniff
access-control-allow-origin
https://www.youtube.com
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
114
date
Wed, 16 Sep 2026 06:45:46 GMT
x-xss-protection
0
content-type
application/json+protobuf; charset=UTF-8
vary
Origin, X-Origin, Referer
server
ESF
x-frame-options
SAMEORIGIN
GET
H2
200
wpartner Show response
ssp.goadservices.com/setuid/ Frame ED54
112 B
528 B
194ms
98ms
Fetch
text/plain
212.77.113.48
WirtualnaPolska W...
General
Full URL
https://ssp.goadservices.com/setuid/wpartner?uid=53df3e2c6c9971933f0b8c6acf715e73:3ac0da:1789541144:v3&host=sklep.doppelherz.pl&bidder=gopl
Requested by
Host: std.wpcdn.pl
URL: https://std.wpcdn.pl/wpjslib6/wpjslib-gosync.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
212.77.113.48 , Poland, ASN12827 (WirtualnaPolska Wirtualna Polska Media S.A., PL),
Reverse DNS
Software
nginx /
Resource Hash
3171af41292a0a68db5f7f26c3580465be72e5e6a0bb3cfdcbdc54254536454b

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://ssp.wp.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

access-control-allow-credentials
true
x-op-id-all
1b1r1d
access-control-allow-origin
https://ssp.wp.pl
content-length
112
date
Wed, 16 Sep 2026 06:45:46 GMT
content-type
text/plain; charset=utf-8
vary
Origin
server
nginx
GET
H2
200
css2
fonts.googleapis.com/
1 KB
609 B
57ms
56ms
Stylesheet
text/css
142.251.14.95
Google LLC
General
Full URL
https://fonts.googleapis.com/css2?family=Archivo:wght@100..900&display=swap
Requested by
Host:
URL: about:client
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
142.251.14.95 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f95.1e100.net
Software
ESF /
Resource Hash
f5cec2af9e0ef8787173dd1c3dac4170d377aedc63c353e1f51299fd1356a050
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-content-type-options
nosniff
expires
Wed, 16 Sep 2026 06:45:46 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 16 Sep 2026 06:45:46 GMT
content-type
text/css; charset=utf-8
vary
Sec-Fetch-Dest, Sec-Fetch-Mode, Sec-Fetch-Site
last-modified
Wed, 16 Sep 2026 06:41:06 GMT
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=31536000
link
<https://fonts.gstatic.com>; rel=preconnect; crossorigin
cache-control
private, max-age=86400, stale-while-revalidate=604800
timing-allow-origin
*
cross-origin-opener-policy
same-origin-allow-popups
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
x-xss-protection
0
server
ESF
GET
H2
200
css2
fonts.googleapis.com/
1 KB
582 B
59ms
58ms
Stylesheet
text/css
142.251.14.95
Google LLC
General
Full URL
https://fonts.googleapis.com/css2?family=Saira:wght@100..900&display=swap
Requested by
Host:
URL: about:client
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
142.251.14.95 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f95.1e100.net
Software
ESF /
Resource Hash
fdc0cf5659fef3148d9f8a0f94e7c0f35d1956cf4b212b2ca85c07d2542d596c
Security Headers
Name Value
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-content-type-options
nosniff
expires
Wed, 16 Sep 2026 06:45:46 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 16 Sep 2026 06:45:46 GMT
content-type
text/css; charset=utf-8
vary
Sec-Fetch-Dest, Sec-Fetch-Mode, Sec-Fetch-Site
last-modified
Wed, 16 Sep 2026 06:34:29 GMT
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=31536000
link
<https://fonts.gstatic.com>; rel=preconnect; crossorigin
cache-control
private, max-age=86400, stale-while-revalidate=604800
timing-allow-origin
*
cross-origin-opener-policy
same-origin-allow-popups
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
x-xss-protection
0
server
ESF
POST
H2
200
binding Show response
sklep.doppelherz.pl/webapi/front/inpost/
98 B
437 B
171ms
170ms
Fetch
application/json
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/webapi/front/inpost/binding
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/assets/js/frontstore/main.ab4429d120a166c61eeb.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
15bcee52d985b176245cc0c630167f32dc498053691861a61deef863c69741d8
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
application/json
sec-ch-ua-mobile
?0

Response headers

cache-control
no-store, no-cache, must-revalidate
content-encoding
gzip
pragma
no-cache
x-shop-session
b8st7bmeks1ihvb7d7sddktjhp
x-content-type-options
nosniff
expires
Thu, 19 Nov 1981 08:52:00 GMT
date
Wed, 16 Sep 2026 06:45:46 GMT
x-xss-protection
1; mode=block
content-type
application/json
x-powered-by
DCSaaS
server
DCSaaS/httpd
GET
H2
200
content Show response
inpostpay-widget-api.inpost.pl/v1/inpostpay/widget/
63 KB
11 KB
93ms
78ms
Fetch
application/json
172.64.146.195
Cloudflare
General
Full URL
https://inpostpay-widget-api.inpost.pl/v1/inpostpay/widget/content?merchantClientId=43a0b7bd-e88a-40f4-9a3d-cfaedf095451
Requested by
Host: inpostpay-widget-v2.inpost.pl
URL: https://inpostpay-widget-v2.inpost.pl/inpostpay.widget.v2.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.64.146.195 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
a0dbfa59c26550e7190a8dc17ec33fbab2de118039e568c4fb323b197f30b34d
Security Headers
Name Value
Strict-Transport-Security max-age=31536000 ; includeSubDomains
X-Content-Type-Options nosniff
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Accept
*/*;version=2.2.0
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-correlation-id
b60377e6-0bb2-404b-a47f-5b390ae567c2
content-encoding
gzip
cf-cache-status
DYNAMIC
access-control-allow-methods
GET,POST,DELETE
x-content-type-options
nosniff
expires
0
alt-svc
h3=":443"; ma=86400
date
Wed, 16 Sep 2026 06:45:46 GMT
content-type
application/json
vary
accept-encoding
x-frame-options
DENY
strict-transport-security
max-age=31536000 ; includeSubDomains
cache-control
no-cache, no-store, max-age=0, must-revalidate
pragma
no-cache
access-control-allow-credentials
true
referrer-policy
no-referrer
via
1.1 google
cf-ray
a3bde902da73ccaf-WAW
access-control-allow-origin
https://sklep.doppelherz.pl
server
cloudflare
GET
H2
200
cb=gapi.loaded_0 Show response
apis.google.com/_/scs/abc-static/_/js/k=gapi.lb.pl.r2bYKzcHidM.O/m=gapi_iframes,gapi_iframes_style_common/rt=j/sv=1/d=1/ed=1/rs=AHpOoo_W5oST4w0nWzAS8ntjYKme90h9Wg/ Frame 0227
132 KB
44 KB
47ms
47ms
Script
text/javascript
142.251.14.113
Google LLC
General
Full URL
https://apis.google.com/_/scs/abc-static/_/js/k=gapi.lb.pl.r2bYKzcHidM.O/m=gapi_iframes,gapi_iframes_style_common/rt=j/sv=1/d=1/ed=1/rs=AHpOoo_W5oST4w0nWzAS8ntjYKme90h9Wg/cb=gapi.loaded_0?le=scs,fedcm_migration_mod
Requested by
Host: apis.google.com
URL: https://apis.google.com/js/api.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.14.113 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f113.1e100.net
Software
sffe /
Resource Hash
727eb2f382eb0c30f6b759072b16185eaec93666000960f7fbc5a384f66c4b1e
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.google.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
age
399452
report-to
{"group":"social-frontend-mpm-access","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/social-frontend-mpm-access"}]}
x-content-type-options
nosniff
expires
Sat, 11 Sep 2027 15:48:14 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 11 Sep 2026 15:48:14 GMT
last-modified
Sun, 02 Aug 2026 15:19:54 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
cache-control
public, max-age=31536000
cross-origin-opener-policy
same-origin; report-to="social-frontend-mpm-access"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/social-frontend-mpm-access
accept-ranges
bytes
access-control-allow-origin
*
content-length
44277
x-xss-protection
0
server
sffe
GET
H2
200
/
rtb-csync.smartadserver.com/redir/ Frame ED54
43 B
600 B
287ms
125ms
Image
image/gif
81.17.55.173
LEASEWEB-NL-AMS-0...
General
Full URL
https://rtb-csync.smartadserver.com/redir/?partnerid=55&gdpr=0&partneruserid=53df3e2c6c9971933f0b8c6acf715e73:3ac0da:1789541144:v3
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
81.17.55.173 , Netherlands, ASN60781 (LEASEWEB-NL-AMS-01 LeaseWeb Netherlands B.V., NL),
Reverse DNS
Software
/
Resource Hash
89fe0ee6020314794fc2cfeacf3d10c31050cfe56f8ebddf1ed0a33fbe941fa7

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://ssp.wp.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache,no-store
p3p
CP="BUS CUR CONo FIN IVDo ONL OUR PHY SAMo TELo"
date
Wed, 16 Sep 2026 06:45:45 GMT
pragma
no-cache
content-type
image/gif
GET
H3
200
pixel
cm.g.doubleclick.net/ Frame ED54
Redirect Chain
  • https://cm.g.doubleclick.net/pixel?google_nid=gopl_sp_z_oo&process_consent=T&google_ula=9190014480&google_hm=Z28tMDFNMk1GRFFHQjQ5SEtUUVA3NzFQVzhXM0c=
  • https://cm.g.doubleclick.net/pixel?google_nid=gopl_sp_z_oo&process_consent=T&google_ula=9190014480&google_hm=Z28tMDFNMk1GRFFHQjQ5SEtUUVA3NzFQVzhXM0c=&google_tc=
170 B
188 B
69ms
69ms
Image
image/png
142.251.110.154
Google LLC
General
Full URL
https://cm.g.doubleclick.net/pixel?google_nid=gopl_sp_z_oo&process_consent=T&google_ula=9190014480&google_hm=Z28tMDFNMk1GRFFHQjQ5SEtUUVA3NzFQVzhXM0c=&google_tc=
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H3
Server
142.251.110.154 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f154.1e100.net
Software
HTTP server (unknown) /
Resource Hash
0b8a20373c6dd04e091902226d922b3688143a8938afb9d283d889de7b55ceb5
Security Headers
Name Value
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer
https://ssp.wp.pl/

Response headers

cache-control
no-cache, must-revalidate
pragma
no-cache
cross-origin-resource-policy
cross-origin
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
170
date
Wed, 16 Sep 2026 06:45:46 GMT
x-xss-protection
0
content-type
image/png
server
HTTP server (unknown)

Redirect headers

cache-control
no-cache, must-revalidate
location
https://cm.g.doubleclick.net/pixel?google_nid=gopl_sp_z_oo&process_consent=T&google_ula=9190014480&google_hm=Z28tMDFNMk1GRFFHQjQ5SEtUUVA3NzFQVzhXM0c=&google_tc=
pragma
no-cache
cross-origin-resource-policy
cross-origin
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
content-length
373
date
Wed, 16 Sep 2026 06:45:46 GMT
x-xss-protection
0
content-type
text/html; charset=UTF-8
server
HTTP server (unknown)
GET
H2
200
match
c1.adform.net/serving/cookie/ Frame ED54
Redirect Chain
  • https://c1.adform.net/serving/cookie/match?party=10013&gdpr=0&cid=53df3e2c6c9971933f0b8c6acf715e73:3ac0da:1789541144:v3
  • https://c1.adform.net/serving/cookie/match?CC=1&party=10013&gdpr=0&cid=53df3e2c6c9971933f0b8c6acf715e73:3ac0da:1789541144:v3
35 B
600 B
114ms
113ms
Image
image/gif
37.157.2.13
ADFORM Adform A/S
General
Full URL
https://c1.adform.net/serving/cookie/match?CC=1&party=10013&gdpr=0&cid=53df3e2c6c9971933f0b8c6acf715e73:3ac0da:1789541144:v3
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Server
37.157.2.13 , Denmark, ASN198622 (ADFORM Adform A/S, DK),
Reverse DNS
Software
nginx /
Resource Hash
8337212354871836e6763a41e615916c89bac5b3f1f0adf60ba43c7c806e1015
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer
https://ssp.wp.pl/

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
access-control-max-age
86400
cache-control
no-cache, no-store, must-revalidate, no-transform
pragma
no-cache
accept-ch
Sec-CH-UA,Sec-CH-UA-Arch,Sec-CH-UA-Bitness,Sec-CH-UA-Full-Version-List,Sec-CH-UA-Mobile,Sec-CH-UA-Model,Sec-CH-UA-Platform,Sec-CH-UA-Platform-Version
access-control-allow-credentials
true
access-control-allow-methods
GET
expires
-1
access-control-allow-origin
*
date
Wed, 16 Sep 2026 06:45:46 GMT
content-type
image/gif
server
nginx
access-control-allow-headers
Content-Type,Cache-Control,Accept-Encoding,X-Requested-With

Redirect headers

strict-transport-security
max-age=31536000; includeSubDomains
access-control-max-age
86400
cache-control
no-cache, no-store, must-revalidate, no-transform
location
https://c1.adform.net/serving/cookie/match?CC=1&party=10013&gdpr=0&cid=53df3e2c6c9971933f0b8c6acf715e73:3ac0da:1789541144:v3
pragma
no-cache
accept-ch
Sec-CH-UA,Sec-CH-UA-Arch,Sec-CH-UA-Bitness,Sec-CH-UA-Full-Version-List,Sec-CH-UA-Mobile,Sec-CH-UA-Model,Sec-CH-UA-Platform,Sec-CH-UA-Platform-Version
access-control-allow-credentials
true
access-control-allow-methods
GET
expires
-1
access-control-allow-origin
*
content-length
0
date
Wed, 16 Sep 2026 06:45:46 GMT
server
nginx
access-control-allow-headers
Content-Type,Cache-Control,Accept-Encoding,X-Requested-With
GET
H3
200
rum
dsum-sec.casalemedia.com/ Frame ED54
Redirect Chain
  • https://dsum-sec.casalemedia.com/rum?cm_dsp_id=264&gdpr=0&external_user_id=go-01M2MFDQGB49HKTQP771PW8W3G
  • https://dsum-sec.casalemedia.com/rum?cm_dsp_id=264&gdpr=0&external_user_id=go-01M2MFDQGB49HKTQP771PW8W3G&C=1
43 B
744 B
59ms
59ms
Image
image/gif
104.18.27.193
Cloudflare
General
Full URL
https://dsum-sec.casalemedia.com/rum?cm_dsp_id=264&gdpr=0&external_user_id=go-01M2MFDQGB49HKTQP771PW8W3G&C=1
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H3
Server
104.18.27.193 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
b1442e85b03bdcaf66dc58c7abb98745dd2687d86350be9a298a1d9382ac849b

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer
https://ssp.wp.pl/

Response headers

cache-control
no-cache
nel
{"report_to":"cf-nel","success_fraction":0.01,"max_age":604800}
cf-cache-status
DYNAMIC
pragma
no-cache
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=nmLXgtu3xrnVlj%2B4JqQ4vktO8cFHRtxvTV5kcwRggcUd5wGrbOYnDHKJYg5AYWU3KuKmyvF%2FiXytvsz6fJApw3xZvIiEpnekk2rrNK%2FjP48g3ZhBgFmzBNm4XtOjAMFN%2B5gkwiaG5WphRw%3D%3D"}]}
cf-ray
a3bde904ce55bf60-WAW
expires
0
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
content-length
43
p3p
policyref="/w3c/p3p.xml", CP="NOI DSP COR DEVa TAIa OUR BUS UNI"
date
Wed, 16 Sep 2026 06:45:46 GMT
content-type
image/gif
server
cloudflare
priority
u=3,i

Redirect headers

cache-control
no-cache
location
/rum?cm_dsp_id=264&gdpr=0&external_user_id=go-01M2MFDQGB49HKTQP771PW8W3G&C=1
cf-cache-status
DYNAMIC
pragma
no-cache
nel
{"report_to":"cf-nel","success_fraction":0.01,"max_age":604800}
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=vNc7r1Cy6jnf3A4hHZrpDtO%2FZdHZKl7VjYFPnfc7RFdFUy2Ul2GCXIpoeYsVfhPOYWAPpyTqSoimrf%2FCOKbFDHW5MC%2ForogwpDlKMp6Ro3ZCcrwyXDqNl%2BGdxNrC%2FIlK313z0YIuAQ8CnQ%3D%3D"}]}
cf-ray
a3bde9043e17bf60-WAW
expires
0
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
content-length
0
p3p
policyref="/w3c/p3p.xml", CP="NOI DSP COR DEVa TAIa OUR BUS UNI"
date
Wed, 16 Sep 2026 06:45:46 GMT
server
cloudflare
priority
u=3,i
GET
H2
200
Pug
image2.pubmatic.com/AdServer/ Frame ED54
0
252 B
215ms
72ms
Image
text/html
103.231.98.109
PubMatic
General
Full URL
https://image2.pubmatic.com/AdServer/Pug?vcode=bz0yJnR5cGU9MSZjb2RlPTQxNTgmdGw9MTI5NjAw&gdpr=0&piggybackCookie=53df3e2c6c9971933f0b8c6acf715e73:3ac0da:1789541144:v3
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
103.231.98.109 , Japan, ASN62713 (AS-PUBMATIC - PubMatic, Inc., US),
Reverse DNS
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=16070400; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://ssp.wp.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=16070400; includeSubDomains
cache-control
no-store, no-cache, private
p3p
CP="NOI DSP COR LAW CUR ADMo DEVo TAIo PSAo PSDo IVAo IVDo HISo OTPo OUR SAMo BUS UNI COM NAV INT DEM CNT STA PRE LOC"
content-encoding
gzip
date
Wed, 16 Sep 2026 06:45:46 GMT
content-type
text/html; charset=utf-8
server
nginx
OPTIONS
H2
200
_dfids
eu1-search.doofinder.com/6/dd2861abe315cd888b92f6e181f2678b/ Frame
0
0
350ms
178ms
Preflight
text/plain
18.200.137.183
Amazon.com
General
Full URL
https://eu1-search.doofinder.com/6/dd2861abe315cd888b92f6e181f2678b/_dfids
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
18.200.137.183 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-18-200-137-183.eu-west-1.compute.amazonaws.com
Software
Cowboy /
Resource Hash

Request headers

Accept
*/*
Access-Control-Request-Headers
content-type
Access-Control-Request-Method
POST
Origin
https://sklep.doppelherz.pl
Sec-Fetch-Mode
cors
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36

Response headers

access-control-allow-headers
Origin, Content-Type, Authorization
access-control-allow-methods
POST, GET, PUT, DELETE, PATCH, OPTIONS
access-control-allow-origin
*
allow
POST, GET, PUT, DELETE, PATCH, OPTIONS
cache-control
max-age=0, private, must-revalidate
content-length
0
content-type
text/plain; charset=utf-8
date
Wed, 16 Sep 2026 06:45:46 GMT
server
Cowboy
vary
accept-encoding
x-request-id
GNW6MPoJG69sFsQerJPj
POST
H2
200
_dfids Show response
eu1-search.doofinder.com/6/dd2861abe315cd888b92f6e181f2678b/
172 B
374 B
111ms
109ms
Fetch
application/json
18.200.137.183
Amazon.com
General
Full URL
https://eu1-search.doofinder.com/6/dd2861abe315cd888b92f6e181f2678b/_dfids
Requested by
Host: cdn.doofinder.com
URL: https://cdn.doofinder.com/apps/loader/2.x/loader.min.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
18.200.137.183 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-18-200-137-183.eu-west-1.compute.amazonaws.com
Software
Cowboy /
Resource Hash
ccab4f569710043cb41590788256e2da858d4939f872352a902b8d0a90533d17

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
content-type
application/json
sec-ch-ua-mobile
?0

Response headers

x-request-id
GNW6MQKhbdg9l-AagyXE
cache-control
max-age=0, private, must-revalidate
access-control-allow-origin
*
content-length
172
date
Wed, 16 Sep 2026 06:45:46 GMT
content-type
application/json; charset=utf-8
vary
accept-encoding
server
Cowboy
GET
H2
200
dflayer.min.js Show response
cdn.doofinder.com/livelayer/1.8.194/js/
266 KB
88 KB
83ms
82ms
Script
text/javascript
195.181.175.40
CDN77 Datacamp Li...
General
Full URL
https://cdn.doofinder.com/livelayer/1.8.194/js/dflayer.min.js?v=1.8.194
Requested by
Host: cdn.doofinder.com
URL: https://cdn.doofinder.com/apps/loader/2.x/loader.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
195.181.175.40 Frankfurt am Main, Germany, ASN60068 (CDN77 Datacamp Limited, GB),
Reverse DNS
824291365.fra.cdn77.com
Software
CDN77-Turbo /
Resource Hash
0715f063788e713bb8f23239537c1c5c3b5c8ecdc5a28d789dc6ef35a25079ca

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
W/"b3d7418a95149222e05ed7710d5bbbd6"
age
3
x-77-cache
HIT
date
Wed, 16 Sep 2026 06:45:46 GMT
x-rgw-object-type
Normal
content-type
text/javascript; charset=utf-8
last-modified
Tue, 15 Sep 2026 12:15:24 GMT
x-77-nzt-ray
25b0213183f355e63f3baa6a3545b60e
vary
Accept-Encoding
x-77-nzt
k4o6PqSwmR5A86tRmsZdPBIaXOziCNZw9t1vlNZdu9ohlMSb8++Pu14ese0VopNHAA
cache-control
s-maxage=2592000, max-age=2592000
x-amz-request-id
tx000004e59634f63a9ba71-006aa9371d-c80461d-prg
x-77-pop
frankfurtDE
x-77-age
66554
server
CDN77-Turbo
GET
H2
200
common.css
cdn.doofinder.com/livelayer/1.8.194/css/2/
109 KB
20 KB
65ms
64ms
Stylesheet
text/css
195.181.175.40
CDN77 Datacamp Li...
General
Full URL
https://cdn.doofinder.com/livelayer/1.8.194/css/2/common.css?v=1.8.194
Requested by
Host: cdn.doofinder.com
URL: https://cdn.doofinder.com/apps/loader/2.x/loader.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
195.181.175.40 Frankfurt am Main, Germany, ASN60068 (CDN77 Datacamp Limited, GB),
Reverse DNS
824291365.fra.cdn77.com
Software
CDN77-Turbo /
Resource Hash
b1e3a326b58cd12e602331835447ca917f15158de3d667dbd234cca3ece8e546

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
W/"5dd678f536be314dc40fa2d51918338b"
age
3
x-77-cache
HIT
date
Wed, 16 Sep 2026 06:45:46 GMT
x-rgw-object-type
Normal
content-type
text/css; charset=utf-8
last-modified
Tue, 15 Sep 2026 12:15:24 GMT
x-77-nzt-ray
25b0213183f355e63f3baa6a3872ae0e
vary
Accept-Encoding
x-77-nzt
k9OpQMndzsVxoedZzub1K1/dp1iHBB7RWEpMtlhxo2P5BPOaToY+KHrojcas4C8eVg
cache-control
s-maxage=2592000, max-age=2592000
x-amz-request-id
tx000004ddfbf580198ade9-006aa9371d-c805c32-prg
x-77-pop
frankfurtDE
x-77-age
66554
server
CDN77-Turbo
GET
H2
200
classic.css
cdn.doofinder.com/livelayer/1.8.194/css/2/
6 KB
2 KB
68ms
67ms
Stylesheet
text/css
195.181.175.40
CDN77 Datacamp Li...
General
Full URL
https://cdn.doofinder.com/livelayer/1.8.194/css/2/classic.css?v=1.8.194
Requested by
Host: cdn.doofinder.com
URL: https://cdn.doofinder.com/apps/loader/2.x/loader.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
195.181.175.40 Frankfurt am Main, Germany, ASN60068 (CDN77 Datacamp Limited, GB),
Reverse DNS
824291365.fra.cdn77.com
Software
CDN77-Turbo /
Resource Hash
8d1923ba5c9d3c5c95a94e0fec5d32b7fea8b0e2e48e6491a6b5c054ebec067b

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
W/"68057e3eccabb37c3f7719a35541a635"
age
7
x-77-cache
HIT
date
Wed, 16 Sep 2026 06:45:46 GMT
x-rgw-object-type
Normal
content-type
text/css; charset=utf-8
last-modified
Tue, 15 Sep 2026 12:15:24 GMT
x-77-nzt-ray
25b0213183f355e63f3baa6a5bcfb20e
vary
Accept-Encoding
x-77-nzt
k0rJCDXt0CcWptd9S+NN7rfW4x5pT5FnfRp0UWlrMIcyxAHukd0DGkrwLI0ZzOU+hw
cache-control
s-maxage=2592000, max-age=2592000
x-amz-request-id
tx000002ea67fe2af92921e-006aa9371e-c7d750c-prg
x-77-pop
frankfurtDE
x-77-age
66549
server
CDN77-Turbo
GET
H2
200
recommendations.min.js Show response
cdn.doofinder.com/recommendations-v2/0.4.11/
11 KB
5 KB
186ms
78ms
Script
text/javascript
195.181.175.40
CDN77 Datacamp Li...
General
Full URL
https://cdn.doofinder.com/recommendations-v2/0.4.11/recommendations.min.js?v=0.4.11
Requested by
Host: cdn.doofinder.com
URL: https://cdn.doofinder.com/apps/loader/2.x/loader.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
195.181.175.40 Frankfurt am Main, Germany, ASN60068 (CDN77 Datacamp Limited, GB),
Reverse DNS
824291365.fra.cdn77.com
Software
CDN77-Turbo /
Resource Hash
2e2fff74ced6664bcf4e19a8dd4351121e7b1fb3a8f892434cb139351cf7c829

Request headers

Origin
https://sklep.doppelherz.pl
sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
W/"482160e42caa449edfd0290ddc3801d0"
x-77-cache
HIT
date
Wed, 16 Sep 2026 06:45:46 GMT
x-rgw-object-type
Normal
content-type
text/javascript; charset=utf-8
last-modified
Mon, 27 Jul 2026 10:07:42 GMT
x-77-nzt-ray
25b02131a1e217253f3baa6aa4508f16
vary
Accept-Encoding, Origin
x-77-nzt
k9yNLirXnl6BZXmYMQqLEmFDpt6JUmgUCwvuU14fi10LpMF700bKtwM5eQ8XsGDWog
cache-control
s-maxage=2592000, max-age=2592000
x-amz-request-id
tx000004825857d0e28ddbb-006a672df0-c804637-prg
access-control-allow-origin
https://sklep.doppelherz.pl
x-77-pop
frankfurtDE
x-77-age
324253
server
CDN77-Turbo
GET
H2
200
recommendations.css
cdn.doofinder.com/recommendations-v2/0.4.11/
8 KB
3 KB
115ms
114ms
Stylesheet
text/css
195.181.175.40
CDN77 Datacamp Li...
General
Full URL
https://cdn.doofinder.com/recommendations-v2/0.4.11/recommendations.css?v=0.4.11
Requested by
Host: cdn.doofinder.com
URL: https://cdn.doofinder.com/apps/loader/2.x/loader.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
195.181.175.40 Frankfurt am Main, Germany, ASN60068 (CDN77 Datacamp Limited, GB),
Reverse DNS
824291365.fra.cdn77.com
Software
CDN77-Turbo /
Resource Hash
252d53b28c2f7a0547c23876dc56846abe13d6a5081a50a347fd265a7d42d383

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
W/"3777f3a904ab3dd4339f068c51db2182"
age
2574
x-77-cache
HIT
date
Wed, 16 Sep 2026 06:45:46 GMT
x-rgw-object-type
Normal
content-type
text/css; charset=utf-8
last-modified
Mon, 27 Jul 2026 10:07:42 GMT
x-77-nzt-ray
25b0213183f355e63f3baa6a3ab02a10
vary
Accept-Encoding
x-77-nzt
k9aJ9VJVzhYGZKvvg9BIJ0YXmaI5CFMaKlH66xBMjSWdVBEaM6zKcyaWurcOVkMXEw
cache-control
s-maxage=2592000, max-age=2592000
x-amz-request-id
tx00000dba8559c227b468a-006a672def-c7dff30-prg
x-77-pop
frankfurtDE
x-77-age
1802281
server
CDN77-Turbo
GET
H2
200
shoper.js Show response
cdn.doofinder.com/plugins/
3 KB
2 KB
115ms
115ms
Script
text/javascript
195.181.175.40
CDN77 Datacamp Li...
General
Full URL
https://cdn.doofinder.com/plugins/shoper.js
Requested by
Host: cdn.doofinder.com
URL: https://cdn.doofinder.com/apps/loader/2.x/loader.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
195.181.175.40 Frankfurt am Main, Germany, ASN60068 (CDN77 Datacamp Limited, GB),
Reverse DNS
824291365.fra.cdn77.com
Software
CDN77-Turbo /
Resource Hash
2dba359a3996c17197c837187e64008c5f28ce57708a56682425d94e8545a76a

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
W/"18a11135bc3e72ef98664f5093d120a9"
age
5
x-77-cache
HIT
date
Wed, 16 Sep 2026 06:45:46 GMT
x-rgw-object-type
Normal
content-type
text/javascript; charset=utf-8
last-modified
Thu, 20 Aug 2026 07:44:49 GMT
x-77-nzt-ray
25b0213183f355e63f3baa6ae85c2d10
vary
Accept-Encoding
x-77-nzt
k5y67wiG83wzmKm1v2BiPayfJEBlG+2wq9iyUcP7weAfXlGN+y+9xJFvNr00DCOh7Q
cache-control
s-maxage=14400, max-age=14400
x-amz-request-id
tx00000be34184b2380789d-006a86b078-c801d2c-prg
x-77-pop
frankfurtDE
x-77-age
10212
server
CDN77-Turbo
GET
H2
200
widget Show response
inpostpay-widget-api.inpost.pl/v1/inpostpay/
2 KB
986 B
102ms
101ms
Fetch
application/json
172.64.146.195
Cloudflare
General
Full URL
https://inpostpay-widget-api.inpost.pl/v1/inpostpay/widget?merchantClientId=43a0b7bd-e88a-40f4-9a3d-cfaedf095451&basketBindingApiKey=vlmWYDlLiVKE5SLTaI68og
Requested by
Host: inpostpay-widget-v2.inpost.pl
URL: https://inpostpay-widget-v2.inpost.pl/inpostpay.widget.v2.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.64.146.195 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
5b3334e5d1012f83b1bb44a6d63c132bb908c334bcf8fb8c0800df739eb52c33
Security Headers
Name Value
Strict-Transport-Security max-age=31536000 ; includeSubDomains
X-Content-Type-Options nosniff
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Accept
*/*;version=2.2.0
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-correlation-id
856e253f-88a1-490f-a21f-14f0006011d8
cf-cache-status
DYNAMIC
content-encoding
br
access-control-allow-methods
GET,POST,DELETE
x-content-type-options
nosniff
expires
0
alt-svc
h3=":443"; ma=86400
date
Wed, 16 Sep 2026 06:45:46 GMT
content-type
application/json
x-frame-options
DENY
strict-transport-security
max-age=31536000 ; includeSubDomains
cache-control
no-cache, no-store, max-age=0, must-revalidate
pragma
no-cache
access-control-allow-credentials
true
referrer-policy
no-referrer
via
1.1 google
cf-ray
a3bde9040ccbccaf-WAW
access-control-allow-origin
https://sklep.doppelherz.pl
server
cloudflare
GET
H2
200
storage Show response
api.adquery.io/ Frame B5CE
2 KB
1 KB
127ms
30ms
Document
text/html
51.77.41.26
OVH OVH SAS
General
Full URL
https://api.adquery.io/storage
Requested by
Host: sites.adquery.io
URL: https://sites.adquery.io/js/trackpoint.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
51.77.41.26 Warsaw, Poland, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
Software
nginx /
Resource Hash
7829b459cbc4217a45db28e945b2e452e461d0907a09eb4414cd633f3c8444cd
Security Headers
Name Value
Strict-Transport-Security max-age=63072000

Request headers

Referer
https://sklep.doppelherz.pl/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

access-control-allow-headers
x-requested-with, Content-Type, origin, authorization, accept, client-security-token
access-control-allow-methods
POST, GET, OPTIONS, DELETE, PUT
access-control-allow-origin
*
access-control-max-age
1000
content-encoding
gzip
content-type
text/html
date
Wed, 16 Sep 2026 06:45:46 GMT
etag
W/"67486a10-851"
last-modified
Thu, 28 Nov 2024 13:03:12 GMT
server
nginx
strict-transport-security
max-age=63072000
POST
H2
204
collect
region1.google-analytics.com/g/
0
0
49ms
48ms
Fetch
text/plain
216.239.32.36
Google LLC
General
Full URL
https://region1.google-analytics.com/g/collect?v=2&tid=G-03LP30MEMG&gtm=45je69e1v871169519z8865320812za20gzb865320812zd865320812&_p=1789541144744&gcs=G100&gcd=13q3q3q2q5l1&npa=1&dma_cps=-&dma=1&_eu=AAAAAGAC&cid=904344215.1789541146&frm=0&pscdl=denied&rcb=1&sr=1600x1200&uaa=x86&uab=64&uafvl=Chromium%3B153.0.8010.36%7CGoogle%2520Chrome%3B153.0.8010.36%7CNot_A%2520Brand%3B8.0.0.0&uam=&uamb=0&uap=Linux&uapv=&uaw=0&ul=pl-pl&gaf=2&_s=1&tag_exp=115616985~115938465~115938468~118897920~118897930~120213116~120385423~120469145~120469153&sid=1789541146&sct=1&seg=0&dl=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&dt=Doppelherz%20system%20Kollagen%2011.000%20PLUS%20%7C%2030%20ampu%C5%82ek%20-%20sklep%20Doppelherz&_tu=CA&en=page_view&_fv=1&_ss=1&ep.content_group=sklep.doppelherz.pl&ep.custom_source=(direct)&ep.custom_medium=(none)&ep.custom_campaign=(not%20set)&tfd=2254
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtag/js?id=G-03LP30MEMG&cx=c&gtm=4e69e1
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
216.239.32.36 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
Golfe2 /
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, no-store, must-revalidate
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
content-security-policy-report-only
script-src 'none'; form-action 'none'; frame-src 'none'; report-uri https://csp.withgoogle.com/csp/scaffolding/ascnsrsggc:139:0
report-to
{"group":"ascnsrsggc:139:0","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/scaffolding/ascnsrsggc:139:0"}],}
expires
Fri, 01 Jan 1990 00:00:00 GMT
access-control-allow-origin
https://sklep.doppelherz.pl
cross-origin-opener-policy-report-only
same-origin; report-to=ascnsrsggc:139:0
content-length
0
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 16 Sep 2026 06:45:46 GMT
content-type
text/plain
server
Golfe2
GET

trusted.svg
trustmate.io/images/widgets/badges/v2/pl/
0
0


GET

trusted.svg
trustmate.io/images/widgets/badges/v2/pl/
0
0


GET
H3
200
Gw6kwdfw6UnXLJCcmafZyFRXb3BL9rvi0QZG3Q.woff2
fonts.gstatic.com/s/googlematerialicons/v144/ Frame 0227
228 KB
228 KB
48ms
47ms
Font
font/woff2
192.178.183.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/googlematerialicons/v144/Gw6kwdfw6UnXLJCcmafZyFRXb3BL9rvi0QZG3Q.woff2
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
192.178.183.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfraw-in-f94.1e100.net
Software
sffe /
Resource Hash
b1c44063e9e3fd49af401ac0bc76dbb9c5b059018d43d1e29709e72f3a8a2a6f
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://www.google.com
sec-ch-ua-platform
"Linux"
Referer
https://www.google.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

age
395271
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Sat, 11 Sep 2027 16:57:55 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 11 Sep 2026 16:57:55 GMT
last-modified
Mon, 16 Jun 2025 20:29:51 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
233388
x-xss-protection
0
server
sffe
GET
H3
200
4Ua_rENHsxJlGDuGo1OIlJfC6l_24rlCK1Yo_Iqcsih3SAyH6cAwhX9RFD48TE63OOYKtrwEIJlrpynSEg.woff2
fonts.gstatic.com/s/googlesans/v62/ Frame 0227
13 KB
13 KB
64ms
64ms
Font
font/woff2
192.178.183.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/googlesans/v62/4Ua_rENHsxJlGDuGo1OIlJfC6l_24rlCK1Yo_Iqcsih3SAyH6cAwhX9RFD48TE63OOYKtrwEIJlrpynSEg.woff2
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
192.178.183.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfraw-in-f94.1e100.net
Software
sffe /
Resource Hash
fb968113803313a2acc4da23a43819bfde29ca9d6d2f4964d4a15d55eb0d276b
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://www.google.com
sec-ch-ua-platform
"Linux"
Referer
https://www.google.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

age
394036
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Sat, 11 Sep 2027 17:18:30 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 11 Sep 2026 17:18:30 GMT
last-modified
Tue, 29 Oct 2024 18:38:02 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
13436
x-xss-protection
0
server
sffe
GET
H/1.1
200
OK
p75395.js Show response
dfd.doppelherz.pl/u/37/
77 KB
11 KB
95ms
94ms
Script
application/javascript
95.131.136.1
CLARANET-AS Clara...
General
Full URL
https://dfd.doppelherz.pl/u/37/p75395.js
Requested by
Host: dfd.doppelherz.pl
URL: https://dfd.doppelherz.pl/js/na/na/u/4d647c7fbb.js
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_256_GCM
Server
95.131.136.1 , France, ASN8426 (CLARANET-AS Claranet Limited, GB),
Reverse DNS
front.netaffiliation.net
Software
nginx /
Resource Hash
c2b392d5064f8111106e1a1034d0b716b946a8bc0d9a7811c3209502f0a5d272
Security Headers
Name Value
Strict-Transport-Security max-age=63072000

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

Transfer-Encoding
chunked
Strict-Transport-Security
max-age=63072000
Cache-Control
private, max-age=3600
Content-Encoding
gzip
Connection
keep-alive
Access-Control-Allow-Credentials
true
Referrer-Policy
origin-when-cross-origin
Access-Control-Allow-Origin
*
Date
Wed, 16 Sep 2026 06:45:46 GMT
Content-Type
application/javascript
Vary
Accept-Encoding, Origin
Server
nginx
Access-Control-Allow-Headers
DNT,X-CustomHeader,Keep-Alive,User-Agent,X-Requested-With,If-Modified-Since,Cache-Control,Content-Type,X-Kwanko-Content-Type,X-Kwanko-Sdk-Version,X-KWKunijs-Debug,X-KWKunijs-Version
POST
H3
204
collect
region1.google-analytics.com/g/
0
0
48ms
48ms
Fetch
text/plain
216.239.32.36
Google LLC
General
Full URL
https://region1.google-analytics.com/g/collect?v=2&tid=G-Y3J94C59MN&gtm=45je69e1v871607941z8865320812za20gzb865320812zd865320812&_p=1789541144744&gcs=G100&gcd=13q3q3q2q5l1&npa=1&dma_cps=-&dma=1&_eu=AAAAACAC&cid=904344215.1789541146&frm=0&ibt=1&ngs=1&pscdl=denied&rcb=19&sr=1600x1200&uaa=x86&uab=64&uafvl=Chromium%3B153.0.8010.36%7CGoogle%2520Chrome%3B153.0.8010.36%7CNot_A%2520Brand%3B8.0.0.0&uam=&uamb=0&uap=Linux&uapv=&uaw=0&ul=pl-pl&_s=1&tag_exp=115616986~115938465~115938469~118897920~118897930~120213116~120385423~120469145~120469153&sid=1789541146&sct=1&seg=0&dl=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&dt=Doppelherz%20system%20Kollagen%2011.000%20PLUS%20%7C%2030%20ampu%C5%82ek%20-%20sklep%20Doppelherz&_tu=CA&en=page_view&_fv=1&_ss=1&ep.custom_source=(direct)&ep.custom_medium=(none)&ep.custom_campaign=(not%20set)&tfd=2405
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtag/js?id=G-Y3J94C59MN&cx=c&gtm=4e69e1
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
216.239.32.36 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
Golfe2 /
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, no-store, must-revalidate
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
content-security-policy-report-only
script-src 'none'; form-action 'none'; frame-src 'none'; report-uri https://csp.withgoogle.com/csp/scaffolding/ascnsrsggc:139:0
report-to
{"group":"ascnsrsggc:139:0","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/scaffolding/ascnsrsggc:139:0"}],}
expires
Fri, 01 Jan 1990 00:00:00 GMT
access-control-allow-origin
https://sklep.doppelherz.pl
cross-origin-opener-policy-report-only
same-origin; report-to=ascnsrsggc:139:0
content-length
0
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 16 Sep 2026 06:45:46 GMT
content-type
text/plain
server
Golfe2
GET
H/1.1
200
OK
299secondary_1.svg
static.inpost.pl/izi_images/
12 KB
13 KB
151ms
46ms
Image
image/svg+xml
91.216.25.161
Integer INTEGER.p...
General
Full URL
https://static.inpost.pl/izi_images/299secondary_1.svg
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_128_GCM
Server
91.216.25.161 , Poland, ASN196899 (Integer INTEGER.pl S.A., PL),
Reverse DNS
161.integer.pl
Software
/
Resource Hash
2ee21c7d7831b20eb9727825a46c2b7e609b14afb1531a6ee36921e31a62ccfb
Security Headers
Name Value
Strict-Transport-Security max-age=16070400; includeSubDomains; preload
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

Strict-Transport-Security
max-age=16070400; includeSubDomains; preload
ETag
"3010-65af50c1736d1"
Connection
Keep-Alive
Accept-Ranges
bytes
Access-Control-Allow-Origin
*
Content-Length
12304
Keep-Alive
timeout=5, max=100
Date
Wed, 16 Sep 2026 06:45:46 GMT
X-XSS-Protection
1; mode=block
Last-Modified
Tue, 08 Sep 2026 09:06:16 GMT
Content-Type
image/svg+xml
GET
H/1.1
200
OK
inpostLogo3.svg
static.inpost.pl/izi_images/
5 KB
5 KB
150ms
45ms
Image
image/svg+xml
91.216.25.161
Integer INTEGER.p...
General
Full URL
https://static.inpost.pl/izi_images/inpostLogo3.svg
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_128_GCM
Server
91.216.25.161 , Poland, ASN196899 (Integer INTEGER.pl S.A., PL),
Reverse DNS
161.integer.pl
Software
/
Resource Hash
a9e70abcb6b8e33b7b6b47e3e48ef70d4766af7ac8d473d90840880203d1ac0d
Security Headers
Name Value
Strict-Transport-Security max-age=16070400; includeSubDomains; preload
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

Strict-Transport-Security
max-age=16070400; includeSubDomains; preload
ETag
"120b-653577ad11ce5"
Connection
Keep-Alive
Accept-Ranges
bytes
Access-Control-Allow-Origin
*
Content-Length
4619
Keep-Alive
timeout=5, max=100
Date
Wed, 16 Sep 2026 06:45:46 GMT
X-XSS-Protection
1; mode=block
Last-Modified
Wed, 03 Jun 2026 11:10:48 GMT
Content-Type
image/svg+xml
GET
H3
200
k3kPo8UDI-1M0wlSV9XAw6lQkqWY8Q82sLydOxI.woff2
fonts.gstatic.com/s/archivo/v25/
34 KB
34 KB
48ms
48ms
Font
font/woff2
192.178.183.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/archivo/v25/k3kPo8UDI-1M0wlSV9XAw6lQkqWY8Q82sLydOxI.woff2
Requested by
Host: fonts.googleapis.com
URL: https://fonts.googleapis.com/css2?family=Archivo:wght@100..900&display=swap
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
192.178.183.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfraw-in-f94.1e100.net
Software
sffe /
Resource Hash
8f704806dbedeaaeca334b11ec348bc3ac3a439d6431544b3afb54f534ee4967
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://sklep.doppelherz.pl
sec-ch-ua-platform
"Linux"
Referer
https://fonts.googleapis.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

age
397958
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Sat, 11 Sep 2027 16:13:08 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 11 Sep 2026 16:13:08 GMT
last-modified
Mon, 08 Sep 2025 17:56:47 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
34928
x-xss-protection
0
server
sffe
GET
H3
200
k3kPo8UDI-1M0wlSV9XAw6lQkqWY8Q82sLyTOxK-vA.woff2
fonts.gstatic.com/s/archivo/v25/
32 KB
32 KB
50ms
50ms
Font
font/woff2
192.178.183.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/archivo/v25/k3kPo8UDI-1M0wlSV9XAw6lQkqWY8Q82sLyTOxK-vA.woff2
Requested by
Host: fonts.googleapis.com
URL: https://fonts.googleapis.com/css2?family=Archivo:wght@100..900&display=swap
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
192.178.183.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfraw-in-f94.1e100.net
Software
sffe /
Resource Hash
ff4f17d21930e36d6d93baba663e624cb767afc3feebf7adaebd82242638de05
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://sklep.doppelherz.pl
sec-ch-ua-platform
"Linux"
Referer
https://fonts.googleapis.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

age
397104
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Sat, 11 Sep 2027 16:27:22 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Fri, 11 Sep 2026 16:27:22 GMT
last-modified
Mon, 08 Sep 2025 17:56:47 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
32608
x-xss-protection
0
server
sffe
GET
H2
200
land
t1.adquery.io/traffic/
68 B
100 B
197ms
100ms
Image
image/png
146.59.84.109
OVH OVH SAS
General
Full URL
https://t1.adquery.io/traffic/land?qid=33rszu1m1nzl3847uyy1&ref=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&adqueryRetargetOrderID=56906&time=1789541146459
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
146.59.84.109 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
ns31517745.ip-146-59-84.eu
Software
Apache/2.4.67 (Debian) /
Resource Hash
93ae7d494fad0fb30cbf3ae746a39c4bc7a0f8bbf87fbb587a3f3c01f3c5ce20

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-type
image/png
access-control-max-age
1000
cache-control
max-age=0, must-revalidate, private
access-control-allow-methods
POST, GET, OPTIONS, DELETE, PUT
expires
Wed, 16 Sep 2026 06:45:46 GMT
accept-ranges
bytes
access-control-allow-origin
*
date
Wed, 16 Sep 2026 06:45:46 GMT
content-disposition
inline; filename="1px.png"
vary
Origin
server
Apache/2.4.67 (Debian)
last-modified
Wed, 16 Sep 2026 06:06:41 GMT
access-control-allow-headers
x-requested-with, Content-Type, origin, authorization, accept, client-security-token
POST
H2
200
e3ae8c99-03e2-4aff-b66a-2792e1453102 Show response
eu1-recommendations.doofinder.com/api/widget/
21 KB
4 KB
200ms
199ms
Fetch
text/html
34.249.139.175
Amazon.com
General
Full URL
https://eu1-recommendations.doofinder.com/api/widget/e3ae8c99-03e2-4aff-b66a-2792e1453102
Requested by
Host: cdn.doofinder.com
URL: https://cdn.doofinder.com/recommendations-v2/0.4.11/recommendations.min.js?v=0.4.11
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.249.139.175 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-34-249-139-175.eu-west-1.compute.amazonaws.com
Software
/
Resource Hash
31010610920112383dbc36f5afadd6a3b5be355f7046e8f64e98f1b154a8ce07
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Accept
text/html
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
application/json
sec-ch-ua-mobile
?0

Response headers

x-request-id
GNW6MRQeR_u-vl9jN_Pi
cache-control
max-age=0, private, must-revalidate
access-control-expose-headers
content-encoding
zstd
x-permitted-cross-domain-policies
none
access-control-allow-credentials
true
referrer-policy
strict-origin-when-cross-origin
x-content-type-options
nosniff
x-download-options
noopen
access-control-allow-origin
https://sklep.doppelherz.pl
content-length
3255
date
Wed, 16 Sep 2026 06:45:46 GMT
content-type
text/html; charset=utf-8
vary
accept-encoding
x-frame-options
SAMEORIGIN
OPTIONS
H2
204
e3ae8c99-03e2-4aff-b66a-2792e1453102
eu1-recommendations.doofinder.com/api/widget/ Frame
0
0
317ms
137ms
Preflight
34.249.139.175
Amazon.com
General
Full URL
https://eu1-recommendations.doofinder.com/api/widget/e3ae8c99-03e2-4aff-b66a-2792e1453102
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.249.139.175 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-34-249-139-175.eu-west-1.compute.amazonaws.com
Software
/
Resource Hash

Request headers

Accept
*/*
Access-Control-Request-Headers
content-type
Access-Control-Request-Method
POST
Origin
https://sklep.doppelherz.pl
Sec-Fetch-Mode
cors
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36

Response headers

access-control-allow-credentials
true
access-control-allow-headers
Authorization,Content-Type,Accept,Origin,User-Agent,DNT,Cache-Control,X-Mx-ReqToken,Keep-Alive,X-Requested-With,If-Modified-Since,X-CSRF-Token
access-control-allow-methods
GET,POST,PUT,PATCH,DELETE,OPTIONS
access-control-allow-origin
*
access-control-expose-headers
access-control-max-age
1728000
cache-control
max-age=0, private, must-revalidate
date
Wed, 16 Sep 2026 06:45:46 GMT
x-request-id
GNW6MQcIr_76E1RnNGnB
GET
H2
200
con
t1.adquery.io/traffic/
68 B
412 B
188ms
100ms
Image
image/png
146.59.84.109
OVH OVH SAS
General
Full URL
https://t1.adquery.io/traffic/con?qid=33rszu1m1nzl3847uyy1&conversionCodeId=adq-1234&eventName=landing&ref=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&adqueryRetargetOrderID=56906&time=1789541146469
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
146.59.84.109 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
ns31517745.ip-146-59-84.eu
Software
Apache/2.4.67 (Debian) /
Resource Hash
93ae7d494fad0fb30cbf3ae746a39c4bc7a0f8bbf87fbb587a3f3c01f3c5ce20

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-type
image/png
access-control-max-age
1000
cache-control
max-age=0, must-revalidate, private
access-control-allow-methods
POST, GET, OPTIONS, DELETE, PUT
expires
Wed, 16 Sep 2026 06:45:46 GMT
accept-ranges
bytes
access-control-allow-origin
*
date
Wed, 16 Sep 2026 06:45:46 GMT
content-disposition
inline; filename="1px.png"
vary
Origin
server
Apache/2.4.67 (Debian)
last-modified
Wed, 16 Sep 2026 06:06:41 GMT
access-control-allow-headers
x-requested-with, Content-Type, origin, authorization, accept, client-security-token
GET
H3
200
destination Show response
www.googletagmanager.com/gtag/
406 KB
141 KB
72ms
72ms
Script
application/javascript
192.178.183.97
Google LLC
General
Full URL
https://www.googletagmanager.com/gtag/destination?id=DC-12904208&cx=c&gtm=4e69e1
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtag/js?id=G-00000000&cx=c&gtm=4e69e1
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
192.178.183.97 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfraw-in-f97.1e100.net
Software
Google Tag Manager /
Resource Hash
cdcd4c0c0f00316e1f630b442a2f23c465bcf83639fe790841abd8a0098e6216
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
zstd
report-to
{"group":"ascgsrsghrgc:71:0","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/scaffolding/ascgsrsghrgc:71:0"}],}
expires
Wed, 16 Sep 2026 06:45:46 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 16 Sep 2026 06:45:46 GMT
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
access-control-allow-headers
Cache-Control
strict-transport-security
max-age=31536000; includeSubDomains
cache-control
private, max-age=900
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
content-security-policy-report-only
script-src 'none'; form-action 'none'; frame-src 'none'; report-uri https://csp.withgoogle.com/csp/scaffolding/ascgsrsghrgc:71:0
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to=ascgsrsghrgc:71:0
content-length
144351
x-xss-protection
0
server
Google Tag Manager
GET
H2
200
collect Show response
tagmanager.sklep.doppelherz.pl/g/
65 B
314 B
390ms
152ms
Fetch
text/plain
49.12.245.74
HETZNER-AS Hetzne...
General
Full URL
https://tagmanager.sklep.doppelherz.pl/g/collect?v=2&tid=G-00000000&gtm=45je69e1z8865320812za20gzb865320812zd865320812&_p=1789541144744&gcs=G100&gcd=13q3q3q2q5l1&npa=1&dma_cps=-&dma=1&ecid=404916103&_fplc=0&cid=904344215.1789541146&frm=0&pscdl=denied&rcb=10&sr=1600x1200&uaa=x86&uab=64&uafvl=Chromium%3B153.0.8010.36%7CGoogle%2520Chrome%3B153.0.8010.36%7CNot_A%2520Brand%3B8.0.0.0&uam=&uamb=0&uap=Linux&uapv=&uaw=0&ul=pl-pl&ur=PL-14&sst.rnd=704081011.1789541146&sst.gch=1&sst.etld=google.pl&sst.gcsub=region1&sst.tft=1789541144744&sst.lpc=180174118&sst.navt=n&sst.ude=0&_s=1&tag_exp=115938465~115938468~118897920~118897930~120385423~120469145~120469153&dl=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&sid=1789541146&sct=1&seg=0&dt=Doppelherz%20system%20Kollagen%2011.000%20PLUS%20%7C%2030%20ampu%C5%82ek%20-%20sklep%20Doppelherz&_tu=DA&en=page_view&_fv=1&_ss=1&gap.sstd=2&tfd=2482&richsstsse
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtag/js?id=G-00000000&cx=c&gtm=4e69e1
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
49.12.245.74 Falkenstein, Germany, ASN24940 (HETZNER-AS Hetzner Online GmbH, DE),
Reverse DNS
static.74.245.12.49.clients.your-server.de
Software
/
Resource Hash
e64954dc34e12c7190cc2338a54b07644ff0f102aa71cc7209bcbb49c3009f7c
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache
x-accel-buffering
no
access-control-allow-credentials
true
x-content-type-options
nosniff
access-control-allow-origin
https://sklep.doppelherz.pl
date
Wed, 16 Sep 2026 06:45:46 GMT
content-type
text/plain
vary
Origin
GET
H2
200
doppelherzpl.jsp Show response
www.upsellit.com/active/
40 KB
12 KB
150ms
31ms
Script
application/x-javascript
34.117.39.58
Google LLC
General
Full URL
https://www.upsellit.com/active/doppelherzpl.jsp
Requested by
Host: www.dwin1.com
URL: https://www.dwin1.com/118697.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.117.39.58 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
58.39.117.34.bc.googleusercontent.com
Software
nginx /
Resource Hash
ae4a852f56445524c99085f0bca7ef0cab6c6f0a31b4ade0b1393fecf0c778c3
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
max-age=86400
content-encoding
gzip
age
56905
via
1.1 google
expires
Wed, 16 Sep 2026 14:57:21 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
12531
date
Tue, 15 Sep 2026 14:57:21 GMT
content-type
application/x-javascript;charset=ISO-8859-1
vary
Accept-Encoding
server
nginx
GET
H3
200
zanox_rtg.aspx Show response
www.mainadv.com/retargeting/live/ Frame F129
760 B
963 B
101ms
57ms
Document
text/html
172.67.159.95
Cloudflare
General
Full URL
https://www.mainadv.com/retargeting/live/zanox_rtg.aspx?Key=ZX&visitorIp=DOPPELHERZ_AWI_PL&pageType=product
Requested by
Host: www.dwin1.com
URL: https://www.dwin1.com/118697.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.67.159.95 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
a31e763cbf129bcc0ad0582eef3b22dee0d82dd80fb0555934f2ae8a1a64a145

Request headers

Referer
https://sklep.doppelherz.pl/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

cache-control
public,max-age=1200
cf-cache-status
DYNAMIC
cf-ray
a3bde906bfabc04c-WAW
content-encoding
zstd
content-type
text/html
date
Wed, 16 Sep 2026 06:45:46 GMT
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
priority
u=0,i
referer
https://informatorbrzeski.pl/
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=0Tgjr%2BN0J4TY2cSCiScstCzGpy4q5nKDuZMWA5kCK7byTaAMe3%2B%2FF04CGU%2FC6dnaoD7dD%2Bla5LLPtjMILRVStVFfn6VXfzKSd6hsJZom3aU5AmEtWmJWkwj3ypNCpBXZv9A%3D"}]}
server
cloudflare
server-timing
cfExtPri
via
1.1 google
GET
H2
200
/ Show response
profiling.veoxa.com/boot/request/
5 KB
2 KB
372ms
155ms
Script
text/javascript
37.27.169.254
HETZNER-AS Hetzne...
General
Full URL
https://profiling.veoxa.com/boot/request/?aid=2764&pid=3539&action=Product&productId=412
Requested by
Host: www.dwin1.com
URL: https://www.dwin1.com/118697.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
37.27.169.254 Helsinki, Finland, ASN24940 (HETZNER-AS Hetzner Online GmbH, DE),
Reverse DNS
static.254.169.27.37.clients.your-server.de
Software
/ PHP/8.0.30
Resource Hash
eb94852847a67a9bbb35b69beb319ed42f3a5e2d4ab53f21db2ed623d5159c86
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
no-store, no-cache, must-revalidate
content-encoding
gzip
pragma
no-cache
expires
Wed, 16 Sep 2026 05:45:46 GMT
content-length
1455
date
Wed, 16 Sep 2026 06:45:46 GMT
content-type
text/javascript;charset=UTF-8
x-powered-by
PHP/8.0.30
vary
Accept-Encoding
last-modified
Wed, 16 Sep 2026 06:45:46 GMT
GET
H2
200
track.js Show response
delivery.clickonometrics.pl/tracker=14648/track/shoppers/product_browsed/%7B%22id%22%3A%22412%22%2C%22price%22%3A%22122.7%22%2C%22in_basket%22%3A%22-1%22%7D/
501 B
1 KB
283ms
126ms
Script
text/javascript
91.134.222.90
OVH OVH SAS
General
Full URL
https://delivery.clickonometrics.pl/tracker=14648/track/shoppers/product_browsed/%7B%22id%22%3A%22412%22%2C%22price%22%3A%22122.7%22%2C%22in_basket%22%3A%22-1%22%7D/track.js
Requested by
Host: www.dwin1.com
URL: https://www.dwin1.com/118697.js
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_256_GCM
Server
91.134.222.90 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
Software
nginx /
Resource Hash
e0934767b60d322ba7e49ac74ad92ae10da86c0f775b0cbe412fffe27950e2f3

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-robots-tag
none
cache-control
no-store, no-cache, must-revalidate, max-age=0, post-check=0, pre-check=0
content-encoding
gzip
pragma
no-cache
expires
Sat, 26 Jul 1997 05:00:00 GMT
date
Wed, 16 Sep 2026 06:45:46 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding, Accept-Encoding
server
nginx
last-modified
Wed, 16 Sep 2026 06:45:46 GMT
GET
H2
200
tm.json Show response
delivery.clickonometrics.pl/service=10095/
0
525 B
258ms
102ms
Script
application/json
91.134.222.90
OVH OVH SAS
General
Full URL
https://delivery.clickonometrics.pl/service=10095/tm.json?sid=10095&cid=178&pid=18683
Requested by
Host: www.dwin1.com
URL: https://www.dwin1.com/118697.js
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_256_GCM
Server
91.134.222.90 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-robots-tag
none
access-control-max-age
1000
cache-control
no-store, no-cache, must-revalidate
content-encoding
gzip
pragma
no-cache
access-control-allow-methods
POST, GET, OPTIONS
expires
Thu, 19 Nov 1981 08:52:00 GMT
access-control-allow-origin
*
date
Wed, 16 Sep 2026 06:45:46 GMT
content-type
application/json; charset=UTF-8
vary
Accept-Encoding, Accept-Encoding
server
nginx
access-control-allow-headers
Content-Type
GET
H2
200
recova_client.min.js Show response
t.nunami.ai/
8 KB
8 KB
204ms
69ms
Script
application/javascript
34.159.90.131
Google LLC
General
Full URL
https://t.nunami.ai/recova_client.min.js?shop=118697
Requested by
Host: www.dwin1.com
URL: https://www.dwin1.com/118697.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.159.90.131 Frankfurt am Main, Germany, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
131.90.159.34.bc.googleusercontent.com
Software
Caddy /
Resource Hash
0725643f343602db374cfdfec1b6d124e88964d21bd6efb7b20104c49e8358c1

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

alt-svc
h3=":443"; ma=2592000
cache-control
max-age=21600
content-length
8506
date
Wed, 16 Sep 2026 06:45:46 GMT
content-type
application/javascript
server
Caddy
GET
H2
200
lantern_global_118697.min.js Show response
lantern.roeyecdn.com/
2 KB
2 KB
249ms
103ms
Script
application/octet-stream
99.84.152.66
Amazon.com
General
Full URL
https://lantern.roeyecdn.com/lantern_global_118697.min.js
Requested by
Host: www.dwin1.com
URL: https://www.dwin1.com/118697.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
99.84.152.66 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-99-84-152-66.fra56.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
988608fac85569df9820a19648f260d4da4514e20de84e886adcad97d8aca7c7

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000
x-amz-version-id
TXkPE1EXerrP_lAwUin3pTDhNWQ.ZjUG
etag
"9ad89cce3b85f0d61b301e3d0663299b"
age
2072828
via
1.1 bfd9180a87cfbe975042cface5eb26e4.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
content-length
1856
x-amz-cf-id
kK-6TdhYu5WEbQsEGV-L0oLoL3dA9qMNVQ48aiWI5ZAYDnpMk7-ccg==
date
Sun, 23 Aug 2026 06:58:39 GMT
content-type
application/octet-stream
last-modified
Tue, 05 Aug 2025 09:15:47 GMT
server
AmazonS3
x-amz-cf-pop
FRA56-P13
POST
H2
204
matomo.php
analytics.queisser.com/
0
82 B
100ms
99ms
Ping
text/html
142.132.237.132
HETZNER-AS Hetzne...
General
Full URL
https://analytics.queisser.com/matomo.php?action_name=Doppelherz%20system%20Kollagen%2011.000%20PLUS%20%7C%2030%20ampu%C5%82ek%20-%20sklep%20Doppelherz&idsite=64&rec=1&r=828644&h=8&m=45&s=46&url=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&_id=c1832cfa1fe065ef&_idn=1&send_image=0&_refts=0&pv_id=d6s6oV&pf_net=142&pf_srv=276&pf_tfr=39&pf_dm1=347&uadata=%7B%22formFactors%22%3A%5B%22Desktop%22%5D%2C%22fullVersionList%22%3A%5B%7B%22brand%22%3A%22Chromium%22%2C%22version%22%3A%22153.0.8010.36%22%7D%2C%7B%22brand%22%3A%22Google%20Chrome%22%2C%22version%22%3A%22153.0.8010.36%22%7D%2C%7B%22brand%22%3A%22Not_A%20Brand%22%2C%22version%22%3A%228.0.0.0%22%7D%5D%2C%22mobile%22%3Afalse%2C%22model%22%3A%22%22%2C%22platform%22%3A%22Linux%22%2C%22platformVersion%22%3A%22%22%7D&pdf=1&qt=0&realp=0&wma=0&fla=0&java=0&ag=0&cookie=1&res=1600x1200
Requested by
Host: analytics.queisser.com
URL: https://analytics.queisser.com/matomo.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.132.237.132 Falkenstein, Germany, ASN24940 (HETZNER-AS Hetzner Online GmbH, DE),
Reverse DNS
static.132.237.132.142.clients.your-server.de
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
application/x-www-form-urlencoded; charset=utf-8
sec-ch-ua-mobile
?0

Response headers

access-control-allow-origin
https://sklep.doppelherz.pl
date
Wed, 16 Sep 2026 06:45:46 GMT
content-type
text/html; charset=UTF-8
server
nginx
access-control-allow-credentials
true
HEAD
H3
200
csp.js Show response
js.smct.io/csp/
0
487 B
86ms
36ms
XHR
text/html
172.66.166.111
Cloudflare
General
Full URL
https://js.smct.io/csp/csp.js
Requested by
Host: smct.co
URL: https://smct.co/tm/?t=sklep.doppelherz.pl
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.66.166.111 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cf-cache-status
HIT
x-amz-version-id
null
age
3373640
access-control-allow-methods
GET, HEAD
expires
Fri, 16 Oct 2026 06:45:46 GMT
alt-svc
h3=":443"; ma=86400
x-cache
Hit from cloudfront
x-amz-cf-id
f7ZE6HRoXu-d06rL0qGI6VJMvcgQqia8UYanGaoRyQmnSdp-Ys1gGw==
date
Wed, 16 Sep 2026 06:45:46 GMT
content-type
text/html
last-modified
Wed, 23 Oct 2019 09:31:23 GMT
vary
Origin,Access-Control-Request-Headers,Access-Control-Request-Method
priority
u=1,i
server-timing
cfExtPri
cache-control
public, max-age=2592000
via
1.1 3356301f07067a98e2508f662ccd34d0.cloudfront.net (CloudFront)
cf-ray
a3bde906d9bd7d8d-WAW
accept-ranges
bytes
access-control-allow-origin
*
x-amz-cf-pop
WAW51-P6
server
cloudflare
GET
H2
200
/ Show response
track.adform.net/Serving/TrackPoint/
838 B
1 KB
332ms
140ms
Script
text/javascript
37.157.4.29
ADFORM Adform A/S
General
Full URL
https://track.adform.net/Serving/TrackPoint/?pm=2936053&ADFPageName=02.2023_PageView_Sklep_DoppelHerz&ADFdivider=%7C&ord=803759535993&ADFtpmode=2&loc=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&Set1=pl-PL%7Cpl-PL%7C1600x1200%7C24
Requested by
Host: s2.adform.net
URL: https://s2.adform.net/banners/scripts/st/trackpoint-async.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
37.157.4.29 , Denmark, ASN198622 (ADFORM Adform A/S, DK),
Reverse DNS
Software
nginx /
Resource Hash
b6a9967e221c29d5fe6122c114ca519aa3899b47e72fe9e0a2f4e0b35dff4883
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
86400
content-encoding
gzip
access-control-allow-methods
GET,POST
expires
-1
p3p
CP="NOI DSP COR NID CURa ADMa DEVa TAIa PSAa PSDa OUR LEG NAV INT"
date
Wed, 16 Sep 2026 06:45:46 GMT
content-type
text/javascript; charset=utf-8
vary
Accept-Encoding
access-control-allow-headers
Content-Type,Cache-Control,Accept-Encoding,X-Requested-With
strict-transport-security
max-age=31536000; includeSubDomains
cache-control
no-cache, no-store, must-revalidate, no-transform
pragma
no-cache
accept-ch
Sec-CH-UA,Sec-CH-UA-Arch,Sec-CH-UA-Bitness,Sec-CH-UA-Full-Version-List,Sec-CH-UA-Mobile,Sec-CH-UA-Model,Sec-CH-UA-Platform,Sec-CH-UA-Platform-Version
access-control-allow-credentials
true
access-control-allow-origin
*
server
nginx
POST

user_sync_status
ssp.wp.pl/v1/ Frame ED54
0
0


GET
H2
200
src=12904208;dc_pre=COH5_aLA8pYDFakpZgkdgWMpPw;type=02;cat=0223_000;rcb=12;ord=6477499443053;npa=1;u6=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus;uaa=x86;uab=64;uafvl=...
ade.googlesyndication.com/ddm/activity/
Redirect Chain
  • https://ade.googlesyndication.com/ddm/activity/src=12904208;type=02;cat=0223_000;rcb=12;ord=6477499443053;npa=1;u6=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus;uaa=x86;...
  • https://ade.googlesyndication.com/ddm/activity/src=12904208;dc_pre=COH5_aLA8pYDFakpZgkdgWMpPw;type=02;cat=0223_000;rcb=12;ord=6477499443053;npa=1;u6=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-s...
42 B
107 B
152ms
152ms
Image
image/gif
192.178.183.157
Google LLC
General
Full URL
https://ade.googlesyndication.com/ddm/activity/src=12904208;dc_pre=COH5_aLA8pYDFakpZgkdgWMpPw;type=02;cat=0223_000;rcb=12;ord=6477499443053;npa=1;u6=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus;uaa=x86;uab=64;uafvl=Chromium%3B153.0.8010.36%7CGoogle%2520Chrome%3B153.0.8010.36%7CNot_A%2520Brand%3B8.0.0.0;uamb=0;uam=;uap=Linux;uapv=;uaw=0;pscdl=denied;frm=0;user_data_mode=a;_tu=KFA;gtm=45fe69e1v9190271573z8865320812za20gzb865320812zd865320812xea;gcs=G100;gcd=13q3q3q2q5l1;dma_cps=-;dma=1;dc_fmt=8;tag_exp=115938465~115938468~118897920~118897930~119791748~120213116~120385422~120469145~120469153;epver=2;~oref=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus?
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Server
192.178.183.157 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfraw-in-f157.1e100.net
Software
cafe /
Resource Hash
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer
https://sklep.doppelherz.pl/

Response headers

cache-control
no-cache, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
42
date
Wed, 16 Sep 2026 06:45:47 GMT
x-xss-protection
0
content-type
image/gif
server
cafe

Redirect headers

cache-control
no-cache, must-revalidate
timing-allow-origin
*
location
https://ade.googlesyndication.com/ddm/activity/src=12904208;dc_pre=COH5_aLA8pYDFakpZgkdgWMpPw;type=02;cat=0223_000;rcb=12;ord=6477499443053;npa=1;u6=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus;uaa=x86;uab=64;uafvl=Chromium%3B153.0.8010.36%7CGoogle%2520Chrome%3B153.0.8010.36%7CNot_A%2520Brand%3B8.0.0.0;uamb=0;uam=;uap=Linux;uapv=;uaw=0;pscdl=denied;frm=0;user_data_mode=a;_tu=KFA;gtm=45fe69e1v9190271573z8865320812za20gzb865320812zd865320812xea;gcs=G100;gcd=13q3q3q2q5l1;dma_cps=-;dma=1;dc_fmt=8;tag_exp=115938465~115938468~118897920~118897930~119791748~120213116~120385422~120469145~120469153;epver=2;~oref=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus?
pragma
no-cache
cross-origin-resource-policy
cross-origin
follow-only-when-prerender-shown
1
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
0
date
Wed, 16 Sep 2026 06:45:46 GMT
x-xss-protection
0
content-type
text/html; charset=UTF-8
server
cafe
GET
H2
200
src=12904208;dc_pre=CLX2_aLA8pYDFQRV5wEdJfQ8Zg;type=02;cat=0223_0;rcb=12;ord=6431953893739;npa=1;u3=Doppelherz%C2%AE%20system%20KOLLAGEN%2011.000%20PLUS%2C%2030%20ampu%C5%82ek%20po%2025ml;u4=122.7;...
ade.googlesyndication.com/ddm/activity/
Redirect Chain
  • https://ade.googlesyndication.com/ddm/activity/src=12904208;type=02;cat=0223_0;rcb=12;ord=6431953893739;npa=1;u3=Doppelherz%C2%AE%20system%20KOLLAGEN%2011.000%20PLUS%2C%2030%20ampu%C5%82ek%20po%202...
  • https://ade.googlesyndication.com/ddm/activity/src=12904208;dc_pre=CLX2_aLA8pYDFQRV5wEdJfQ8Zg;type=02;cat=0223_0;rcb=12;ord=6431953893739;npa=1;u3=Doppelherz%C2%AE%20system%20KOLLAGEN%2011.000%20PL...
42 B
118 B
111ms
111ms
Image
image/gif
192.178.183.157
Google LLC
General
Full URL
https://ade.googlesyndication.com/ddm/activity/src=12904208;dc_pre=CLX2_aLA8pYDFQRV5wEdJfQ8Zg;type=02;cat=0223_0;rcb=12;ord=6431953893739;npa=1;u3=Doppelherz%C2%AE%20system%20KOLLAGEN%2011.000%20PLUS%2C%2030%20ampu%C5%82ek%20po%2025ml;u4=122.7;u6=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus;u7=412;uaa=x86;uab=64;uafvl=Chromium%3B153.0.8010.36%7CGoogle%2520Chrome%3B153.0.8010.36%7CNot_A%2520Brand%3B8.0.0.0;uamb=0;uam=;uap=Linux;uapv=;uaw=0;pscdl=denied;frm=0;user_data_mode=a;_tu=KFA;gtm=45fe69e1v9190271573z8865320812za20gzb865320812zd865320812xea;gcs=G100;gcd=13q3q3q2q5l1;dma_cps=-;dma=1;dc_fmt=8;tag_exp=115938465~115938468~118897920~118897930~119791748~120213116~120385422~120469145~120469153;epver=2;~oref=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus?
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Server
192.178.183.157 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfraw-in-f157.1e100.net
Software
cafe /
Resource Hash
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer
https://sklep.doppelherz.pl/

Response headers

cache-control
no-cache, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
42
date
Wed, 16 Sep 2026 06:45:47 GMT
x-xss-protection
0
content-type
image/gif
server
cafe

Redirect headers

cache-control
no-cache, must-revalidate
timing-allow-origin
*
location
https://ade.googlesyndication.com/ddm/activity/src=12904208;dc_pre=CLX2_aLA8pYDFQRV5wEdJfQ8Zg;type=02;cat=0223_0;rcb=12;ord=6431953893739;npa=1;u3=Doppelherz%C2%AE%20system%20KOLLAGEN%2011.000%20PLUS%2C%2030%20ampu%C5%82ek%20po%2025ml;u4=122.7;u6=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus;u7=412;uaa=x86;uab=64;uafvl=Chromium%3B153.0.8010.36%7CGoogle%2520Chrome%3B153.0.8010.36%7CNot_A%2520Brand%3B8.0.0.0;uamb=0;uam=;uap=Linux;uapv=;uaw=0;pscdl=denied;frm=0;user_data_mode=a;_tu=KFA;gtm=45fe69e1v9190271573z8865320812za20gzb865320812zd865320812xea;gcs=G100;gcd=13q3q3q2q5l1;dma_cps=-;dma=1;dc_fmt=8;tag_exp=115938465~115938468~118897920~118897930~119791748~120213116~120385422~120469145~120469153;epver=2;~oref=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus?
pragma
no-cache
cross-origin-resource-policy
cross-origin
follow-only-when-prerender-shown
1
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
0
date
Wed, 16 Sep 2026 06:45:46 GMT
x-xss-protection
0
content-type
text/html; charset=UTF-8
server
cafe
GET
H3
200
tag-v7.14.0-beta.20.js Show response
js.smct.io/v7.14.0-beta.20/
155 KB
48 KB
65ms
35ms
Script
text/javascript
172.66.166.111
Cloudflare
General
Full URL
https://js.smct.io/v7.14.0-beta.20/tag-v7.14.0-beta.20.js
Requested by
Host: smct.co
URL: https://smct.co/tm/?t=sklep.doppelherz.pl
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.66.166.111 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
c44657b7380949b4297c7a1408865de5e73547c9f63c4cab1fa061942dbc7ac8

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
cf-cache-status
HIT
x-amz-version-id
_gbhihV8T.lKNxdUlwELjx6p3sZOmqv.
etag
W/"09e8134d9b1d79f69ee5c5d2354762a7"
age
764477
alt-svc
h3=":443"; ma=86400
x-cache
Hit from cloudfront
x-amz-cf-id
qwcOqZrwLVuIEADiR60Jtg2K68lqfcbVbpi1LMKSrtOvc8izx3CY6Q==
date
Wed, 16 Sep 2026 06:45:46 GMT
content-type
text/javascript
vary
Accept-Encoding
last-modified
Wed, 08 Jul 2026 14:32:12 GMT
priority
u=3,i=?0
server-timing
cfExtPri
cache-control
max-age=2678400
via
1.1 a8dd9e9343adef1e56ef851739036fec.cloudfront.net (CloudFront)
cf-ray
a3bde9075ddaf9bf-WAW
x-amz-cf-pop
WAW51-P6
server
cloudflare
x-amz-server-side-encryption
AES256
GET

audit.aspx
ban.tangooserver.com/ Frame F129
0
0


GET
H2
200
cookiematch.aspx Show response
ban.tangooserver.com/rtb/google/ Frame E82A
Redirect Chain
  • https://cm.g.doubleclick.net/pixel?google_nid=tangoomedia&google_ula=7241462486&google_cm&cok15=awi_dpp_pl&cnty15=POL&Referrer=https%3a%2f%2fsklep.doppelherz.pl%2f&ty_orderid=&ty_orderamt=0&pdt_id=...
  • https://ban.tangooserver.com/rtb/google/cookiematch.aspx?id=tangoomedia&cok15=awi_dpp_pl&cnty15=POL&Referrer=https%3A%2F%2Fsklep.doppelherz.pl%2F&ty_orderid=&ty_orderamt=0&pdt_id=&pdt_category_list...
88 B
926 B
90ms
57ms
Document
text/html
104.18.31.101
Cloudflare
General
Full URL
https://ban.tangooserver.com/rtb/google/cookiematch.aspx?id=tangoomedia&cok15=awi_dpp_pl&cnty15=POL&Referrer=https%3A%2F%2Fsklep.doppelherz.pl%2F&ty_orderid=&ty_orderamt=0&pdt_id=&pdt_category_list=&token=DOPPELHERZ_AWI_PL&pagetype=product&t=4&ProgramName=DOPPELHERZ_AWI_PL&AudienceId=9898&CampaignId=66742&gdpr=0&BrowserCheck=True&google_gid=CAESEEiSW-Fd8L3g4FnCSbvue8c&google_cver=1&google_ula=7241462486,0
Requested by
Host: www.mainadv.com
URL: https://www.mainadv.com/retargeting/live/zanox_rtg.aspx?Key=ZX&visitorIp=DOPPELHERZ_AWI_PL&pageType=product
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.18.31.101 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
e77ddf6d872e25c6859182b24337ab033d70f34756d5d636c8bd6e8531a6be4d
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://www.mainadv.com/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

cache-control
no-cache, no-store, max-age=0, must-revalidate
cf-cache-status
DYNAMIC
cf-ray
a3bde907cba83463-WAW
content-encoding
gzip
content-type
text/html;charset=ISO-8859-1
date
Wed, 16 Sep 2026 06:45:46 GMT
expires
0
pragma
no-cache
referrer-policy
unsafe-url
server
cloudflare
vary
Origin,Access-Control-Request-Method,Access-Control-Request-Headers
via
1.1 google
x-content-type-options
nosniff
x-xss-protection
0

Redirect headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cache-control
no-cache, must-revalidate
content-length
677
content-type
text/html; charset=UTF-8
cross-origin-resource-policy
cross-origin
date
Wed, 16 Sep 2026 06:45:46 GMT
expires
Fri, 01 Jan 1990 00:00:00 GMT
location
https://ban.tangooserver.com/rtb/google/cookiematch.aspx?id=tangoomedia&cok15=awi_dpp_pl&cnty15=POL&Referrer=https%3A%2F%2Fsklep.doppelherz.pl%2F&ty_orderid=&ty_orderamt=0&pdt_id=&pdt_category_list=&token=DOPPELHERZ_AWI_PL&pagetype=product&t=4&ProgramName=DOPPELHERZ_AWI_PL&AudienceId=9898&CampaignId=66742&gdpr=0&BrowserCheck=True&google_gid=CAESEEiSW-Fd8L3g4FnCSbvue8c&google_cver=1&google_ula=7241462486,0
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
pragma
no-cache
server
HTTP server (unknown)
x-xss-protection
0
OPTIONS
H2
204
visit
eu1-api.doofinder.com/api/v2/stats/ Frame
0
0
313ms
137ms
Preflight
52.19.173.53
Amazon.com
General
Full URL
https://eu1-api.doofinder.com/api/v2/stats/visit
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
52.19.173.53 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-52-19-173-53.eu-west-1.compute.amazonaws.com
Software
Cowboy /
Resource Hash

Request headers

Accept
*/*
Access-Control-Request-Headers
content-type
Access-Control-Request-Method
POST
Origin
https://sklep.doppelherz.pl
Sec-Fetch-Mode
cors
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36

Response headers

access-control-allow-credentials
true
access-control-allow-headers
Authorization,Content-Type,Accept,Origin,User-Agent,DNT,Cache-Control,X-Mx-ReqToken,Keep-Alive,X-Requested-With,If-Modified-Since,X-CSRF-Token
access-control-allow-methods
GET,POST,PUT,PATCH,DELETE,OPTIONS
access-control-allow-origin
*
access-control-expose-headers
access-control-max-age
1728000
cache-control
max-age=0, private, must-revalidate
date
Wed, 16 Sep 2026 06:45:47 GMT
server
Cowboy
x-request-id
GNW6MRoqvL6fdS4AIqfx
POST
H2
200
visit Show response
eu1-api.doofinder.com/api/v2/stats/
23 B
257 B
153ms
152ms
Fetch
application/json
52.19.173.53
Amazon.com
General
Full URL
https://eu1-api.doofinder.com/api/v2/stats/visit
Requested by
Host: cdn.doofinder.com
URL: https://cdn.doofinder.com/apps/loader/2.x/loader.min.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
52.19.173.53 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-52-19-173-53.eu-west-1.compute.amazonaws.com
Software
Cowboy /
Resource Hash
0dd33d7fb1b6511c13d0b43c3459f6735a1fac78e6de60aed669bdcfc9f491b3

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
content-type
application/json
sec-ch-ua-mobile
?0

Response headers

x-request-id
GNW6MSULeVA5QDYAQqVB
access-control-expose-headers
cache-control
max-age=0, private, must-revalidate
access-control-allow-credentials
true
access-control-allow-origin
*
content-length
23
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
application/json; charset=utf-8
server
Cowboy
OPTIONS
H2
200
/
cognito-identity.eu-west-1.amazonaws.com/ Frame
0
0
311ms
137ms
Preflight
52.213.207.85
Amazon.com
General
Full URL
https://cognito-identity.eu-west-1.amazonaws.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
52.213.207.85 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-52-213-207-85.eu-west-1.compute.amazonaws.com
Software
/
Resource Hash
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

Accept
*/*
Access-Control-Request-Headers
content-type,x-amz-target
Access-Control-Request-Method
POST
Origin
https://sklep.doppelherz.pl
Sec-Fetch-Mode
cors
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36

Response headers

access-control-allow-headers
content-type,x-amz-target
access-control-allow-methods
POST
access-control-allow-origin
*
access-control-expose-headers
x-amzn-RequestId,x-amzn-ErrorType,x-amzn-ErrorMessage,Date
access-control-max-age
172800
content-length
0
date
Wed, 16 Sep 2026 06:45:47 GMT
strict-transport-security
max-age=31536000; includeSubDomains
x-amzn-requestid
3b5480af-9455-4a0c-ba50-4963e6f14349
POST
H2
200
/ Show response
cognito-identity.eu-west-1.amazonaws.com/
63 B
316 B
157ms
156ms
XHR
application/x-amz-json-1.1
52.213.207.85
Amazon.com
General
Full URL
https://cognito-identity.eu-west-1.amazonaws.com/
Requested by
Host: js.smct.io
URL: https://js.smct.io/v7.14.0-beta.20/tag-v7.14.0-beta.20.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
52.213.207.85 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-52-213-207-85.eu-west-1.compute.amazonaws.com
Software
/
Resource Hash
f576b04fe1c63a962302864e0237b8fac7304d84ec1eb640a7accca76071c7d9
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
X-AMZ-TARGET
AWSCognitoIdentityService.GetId
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
application/x-amz-json-1.1
sec-ch-ua-mobile
?0

Response headers

x-amzn-requestid
240205ca-32c6-4244-9111-98bfabdc8c16
strict-transport-security
max-age=31536000; includeSubDomains
access-control-allow-origin
*
access-control-expose-headers
x-amzn-RequestId,x-amzn-ErrorType,x-amzn-ErrorMessage,Date
content-length
63
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
application/x-amz-json-1.1
GET

trusted.svg
trustmate.io/images/widgets/badges/v2/pl/
0
0


POST
H2
204
check
p.nunami.ai/popup/
0
0
277ms
143ms
Fetch
35.242.250.78
Google LLC
General
Full URL
https://p.nunami.ai/popup/check
Requested by
Host: t.nunami.ai
URL: https://t.nunami.ai/recova_client.min.js?shop=118697
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
35.242.250.78 Frankfurt am Main, Germany, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
78.250.242.35.bc.googleusercontent.com
Software
Caddy /
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

access-control-allow-origin
*
x-nunami-error
shop disabled
date
Wed, 16 Sep 2026 06:45:47 GMT
vary
Origin
server
Caddy
GET
H2
200
track.php
lantern.roeye.com/
0
181 B
291ms
130ms
Image
image/gif
54.195.115.7
Amazon.com
General
Full URL
https://lantern.roeye.com/track.php?fingerprint=ac2b78c0-fb19-4491-b036-f3202c32a7fb&referrer=&landingpage=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&useragent=Mozilla%2F5.0%20(X11%3B%20Linux%20x86_64)%20AppleWebKit%2F537.36%20(KHTML%2C%20like%20Gecko)%20Chrome%2F153.0.0.0%20Safari%2F537.36&site=sklep.doppelherz.pl
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
54.195.115.7 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-54-195-115-7.eu-west-1.compute.amazonaws.com
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-length
0
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
image/gif
server
nginx
GET
H/1.1
200
OK
set-cookie Show response
sync.clickonometrics.pl/adexchange/ Frame AA99
Redirect Chain
  • https://cm.g.doubleclick.net/pixel?google_nid=360ecom_sp_z_oo_2&google_hm=NTM4MjEwXzM3MzAyMQ&google_cm&process_consent=T&advid=
  • https://sync.clickonometrics.pl/adexchange/set-cookie?id=&advid=&google_gid=CAESEMMi5pC-_P0duSsCwSLeI4c&google_cver=1
35 B
299 B
234ms
89ms
Document
image/gif
91.134.222.93
OVH OVH SAS
General
Full URL
https://sync.clickonometrics.pl/adexchange/set-cookie?id=&advid=&google_gid=CAESEMMi5pC-_P0duSsCwSLeI4c&google_cver=1
Requested by
Host: delivery.clickonometrics.pl
URL: https://delivery.clickonometrics.pl/tracker=14648/track/shoppers/product_browsed/%7B%22id%22%3A%22412%22%2C%22price%22%3A%22122.7%22%2C%22in_basket%22%3A%22-1%22%7D/track.js
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_128_GCM
Server
91.134.222.93 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
Software
nginx /
Resource Hash
6a842ea462daca2a0b5a0f5f25bcfc8e0059ac811ca6c6a1bc54e4d9119621c3

Request headers

Referer
https://sklep.doppelherz.pl/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

cache-control
no-store, no-cache, must-revalidate
connection
close
content-type
image/gif
date
Wed, 16 Sep 2026 06:45:47 GMT
expires
Thu, 19 Nov 1981 08:52:00 GMT
pragma
no-cache
server
nginx
transfer-encoding
chunked

Redirect headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cache-control
no-cache, must-revalidate
content-length
326
content-type
text/html; charset=UTF-8
cross-origin-resource-policy
cross-origin
date
Wed, 16 Sep 2026 06:45:46 GMT
expires
Fri, 01 Jan 1990 00:00:00 GMT
location
https://sync.clickonometrics.pl/adexchange/set-cookie?id=&advid=&google_gid=CAESEMMi5pC-_P0duSsCwSLeI4c&google_cver=1
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
pragma
no-cache
server
HTTP server (unknown)
x-xss-protection
0
GET
H2
200
pixels Show response
c1.adform.net/imatch/ Frame 2542
4 KB
2 KB
72ms
72ms
Document
text/html
37.157.2.13
ADFORM Adform A/S
General
Full URL
https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Requested by
Host: track.adform.net
URL: https://track.adform.net/Serving/TrackPoint/?pm=2936053&ADFPageName=02.2023_PageView_Sklep_DoppelHerz&ADFdivider=%7C&ord=803759535993&ADFtpmode=2&loc=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&Set1=pl-PL%7Cpl-PL%7C1600x1200%7C24
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
37.157.2.13 , Denmark, ASN198622 (ADFORM Adform A/S, DK),
Reverse DNS
Software
nginx /
Resource Hash
28f653cd85eb808ad006e0e5674c09bd269984e6d1fdf4de7e93fbd8caee1894
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

Referer
https://sklep.doppelherz.pl/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

accept-ch
Sec-CH-UA,Sec-CH-UA-Arch,Sec-CH-UA-Bitness,Sec-CH-UA-Full-Version-List,Sec-CH-UA-Mobile,Sec-CH-UA-Model,Sec-CH-UA-Platform,Sec-CH-UA-Platform-Version
access-control-allow-credentials
true
access-control-allow-headers
Content-Type,Cache-Control,Accept-Encoding,X-Requested-With
access-control-allow-methods
GET
access-control-allow-origin
*
access-control-max-age
86400
cache-control
no-cache, no-store, must-revalidate, no-transform
content-encoding
gzip
content-type
text/html; charset=UTF-8
date
Wed, 16 Sep 2026 06:45:47 GMT
expires
-1
pragma
no-cache
server
nginx
strict-transport-security
max-age=31536000; includeSubDomains
vary
Accept-Encoding
GET
H2
200
/
server.seadform.net/serving/cookie/sync/
35 B
676 B
319ms
136ms
Image
image/gif
37.157.6.246
ADFORM Adform A/S
General
Full URL
https://server.seadform.net/serving/cookie/sync/?uid=5351721985196806187&stamp=4Z5nvfGVIiUDvP-67D9Y4w2
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
37.157.6.246 , Denmark, ASN198622 (ADFORM Adform A/S, DK),
Reverse DNS
Software
nginx /
Resource Hash
8337212354871836e6763a41e615916c89bac5b3f1f0adf60ba43c7c806e1015
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
access-control-max-age
86400
cache-control
no-cache, no-store, must-revalidate, no-transform
pragma
no-cache
accept-ch
Sec-CH-UA,Sec-CH-UA-Arch,Sec-CH-UA-Bitness,Sec-CH-UA-Full-Version-List,Sec-CH-UA-Mobile,Sec-CH-UA-Model,Sec-CH-UA-Platform,Sec-CH-UA-Platform-Version
access-control-allow-credentials
true
access-control-allow-methods
GET,POST
expires
-1
access-control-allow-origin
*
p3p
CP="NOI DSP COR NID CURa ADMa DEVa TAIa PSAa PSDa OUR LEG NAV INT"
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
image/gif
vary
*
server
nginx
access-control-allow-headers
Content-Type,Cache-Control,Accept-Encoding,X-Requested-With
GET
H2
200
js Show response
profiling.veoxa.com/store/
723 B
977 B
189ms
188ms
Script
text/javascript
37.27.169.254
HETZNER-AS Hetzne...
General
Full URL
https://profiling.veoxa.com/store/js?aid=2764&pid=3539&action=Product&productId=412&rand=1789541146_665444430&referrer=&charset=UTF-8
Requested by
Host: profiling.veoxa.com
URL: https://profiling.veoxa.com/boot/request/?aid=2764&pid=3539&action=Product&productId=412
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
37.27.169.254 Helsinki, Finland, ASN24940 (HETZNER-AS Hetzner Online GmbH, DE),
Reverse DNS
static.254.169.27.37.clients.your-server.de
Software
/ PHP/8.0.30
Resource Hash
71ac195d6650b7750eebb43459d0ee876634248bcab13c495ca7d35c712856aa
Security Headers
Name Value
Content-Security-Policy default-src 'self' 'unsafe-inline'
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
content-security-policy
default-src 'self' 'unsafe-inline'
cache-control
no-store, no-cache, must-revalidate
content-encoding
gzip
pragma
no-cache
expires
Wed, 16 Sep 2026 05:45:47 GMT
content-length
407
p3p
policyref="https://profiling.veoxa.com/w3c/p3p.xml", CP="NOI CUR OUR STP", policyref="https://profiling.veoxa.com/w3c/p3p.xml", CP="NOI CUR OUR STP"
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
text/javascript;charset=UTF-8
x-powered-by
PHP/8.0.30
vary
Accept-Encoding
last-modified
Wed, 16 Sep 2026 06:45:47 GMT
GET
H2
200
1399.webp
sklep685892.shoparena.pl/userdata/public/gfx/
74 KB
74 KB
239ms
90ms
Image
image/webp
77.79.221.139
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep685892.shoparena.pl/userdata/public/gfx/1399.webp
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.139 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-139.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
d3c033fb8fd265a34e85eeb41df0a73a6ec7865a32ba3be75ec98baedc97a58a
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000
etag
fecefb5e09381eaedfead1977362038c
x-cdn
1
x-content-type-options
nosniff
accept-ranges
bytes
content-length
75596
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
image/webp
last-modified
Thu, 03 Sep 2026 15:34:31 GMT
server
DCSaaS/httpd
x-powered-by
DCSaaS
GET
H2
200
1320.webp
sklep685892.shoparena.pl/userdata/public/gfx/
37 KB
37 KB
194ms
45ms
Image
image/webp
77.79.221.139
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep685892.shoparena.pl/userdata/public/gfx/1320.webp
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.139 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-139.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
625a20fcf54d921900a762961a2ddcefe135ee540a5b95b758fc2dc5eb3bc375
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000
etag
9c3fac15591063ad3346e2a4c69b91fd
x-cdn
1
x-content-type-options
nosniff
accept-ranges
bytes
content-length
37682
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
image/webp
last-modified
Fri, 29 May 2026 10:38:03 GMT
server
DCSaaS/httpd
x-powered-by
DCSaaS
GET
H2
200
1350.webp
sklep685892.shoparena.pl/userdata/public/gfx/
765 KB
766 KB
295ms
146ms
Image
image/webp
77.79.221.139
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep685892.shoparena.pl/userdata/public/gfx/1350.webp
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.139 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-139.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
d3fe90218f83b6f548244d85b0be20ae170b15802a61a3eb193596c0b2d4c748
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000
etag
da71d1e1a6e5e6c64ce28a611d4b2d57
x-cdn
1
x-content-type-options
nosniff
accept-ranges
bytes
content-length
783134
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
image/webp
last-modified
Wed, 24 Jun 2026 09:21:01 GMT
server
DCSaaS/httpd
x-powered-by
DCSaaS
GET
H2
200
1079.webp
sklep685892.shoparena.pl/userdata/public/gfx/
43 KB
43 KB
307ms
158ms
Image
image/webp
77.79.221.139
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep685892.shoparena.pl/userdata/public/gfx/1079.webp
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.139 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-139.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
0ae4bfde2ffb91cb09d871fb260ff96c8c399dbb68e7e6320387ebe57fb17189
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000
etag
55a5c3615c99571f9045739b697422c4
x-cdn
1
x-content-type-options
nosniff
accept-ranges
bytes
content-length
43678
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
image/webp
last-modified
Tue, 03 Mar 2026 14:30:48 GMT
server
DCSaaS/httpd
x-powered-by
DCSaaS
GET
H2
200
1348.webp
sklep685892.shoparena.pl/userdata/public/gfx/
613 KB
614 KB
279ms
130ms
Image
image/webp
77.79.221.139
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep685892.shoparena.pl/userdata/public/gfx/1348.webp
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.139 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-139.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
bd416788a3100151508a9baeb237a9484f7ced0a583a6896836a14c4bbd3057a
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000
etag
9c4b5a2c5f97dd55a5623443c1d0e6e5
x-cdn
1
x-content-type-options
nosniff
accept-ranges
bytes
content-length
627330
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
image/webp
last-modified
Wed, 24 Jun 2026 09:19:57 GMT
server
DCSaaS/httpd
x-powered-by
DCSaaS
GET
H2
200
825.png
sklep685892.shoparena.pl/userdata/public/gfx/
58 KB
58 KB
380ms
231ms
Image
image/png
77.79.221.139
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep685892.shoparena.pl/userdata/public/gfx/825.png
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.139 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-139.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
5e439f78662b66e168243577f73e81eb3a5c7227d2b530142f666d2e3fc2cf9b
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=2592000
etag
5b57f3bf680d318466453b21537d65c4
x-cdn
1
x-content-type-options
nosniff
accept-ranges
bytes
content-length
59333
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
image/png
last-modified
Tue, 03 Mar 2026 14:30:35 GMT
server
DCSaaS/httpd
x-powered-by
DCSaaS
GET
H2
200
plf
c1.adform.net/imatch/ Frame 2542
0
384 B
71ms
71ms
Image
text/plain
37.157.2.13
ADFORM Adform A/S
General
Full URL
https://c1.adform.net/imatch/plf?name=plff
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
37.157.2.13 , Denmark, ASN198622 (ADFORM Adform A/S, DK),
Reverse DNS
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
access-control-max-age
86400
accept-ch
Sec-CH-UA,Sec-CH-UA-Arch,Sec-CH-UA-Bitness,Sec-CH-UA-Full-Version-List,Sec-CH-UA-Mobile,Sec-CH-UA-Model,Sec-CH-UA-Platform,Sec-CH-UA-Platform-Version
access-control-allow-credentials
true
access-control-allow-methods
GET
access-control-allow-origin
*
date
Wed, 16 Sep 2026 06:45:47 GMT
server
nginx
access-control-allow-headers
Content-Type,Cache-Control,Accept-Encoding,X-Requested-With
GET
H2
200
match
ad.360yield.com/ Frame 2542
43 B
199 B
317ms
136ms
Image
image/gif
34.241.233.208
Amazon.com
General
Full URL
https://ad.360yield.com/match?publisher_dsp_id=42&external_user_id=5351721985196806187&Expiration=1790750747
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.241.233.208 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-34-241-233-208.eu-west-1.compute.amazonaws.com
Software
/
Resource Hash
548f2d6f4d0d820c6c5ffbeffcbd7f0e73193e2932eefe542accc84762deec87

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://c1.adform.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

access-control-allow-origin
*
p3p
CP="NOI DSP COR NID CURa ADMa DEVa PSAa PSDa OUR BUS COM INT OTC PUR STA"
content-length
43
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
image/gif
GET
H/1.1
204
No Content
m
ad.yieldlab.net/ Frame 2542
0
235 B
312ms
176ms
Image
text/plain
88.221.170.40
Akamai Technologies
General
Full URL
https://ad.yieldlab.net/m?dt_id=4879&ext_id=5351721985196806187
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_256_GCM
Server
88.221.170.40 Frankfurt am Main, Germany, ASN16625 (AKAMAI-AS - Akamai Technologies, Inc., US),
Reverse DNS
a88-221-170-40.deploy.static.akamaitechnologies.com
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://c1.adform.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

Expires
Tue, 15 Sep 2026 06:45:47 GMT
Cache-Control
no-store,no-cache,max-age=-3600,must-revalidate,post-check=0,pre-check=0
Pragma
no-cache
Date
Wed, 16 Sep 2026 06:45:47 GMT
Connection
keep-alive
GET
H/1.1
204
No Content
token
token.rubiconproject.com/ Frame 2542
0
214 B
221ms
47ms
Image
text/plain
69.173.144.138
Magnite
General
Full URL
https://token.rubiconproject.com/token?pid=5232&puid=5351721985196806187
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
HTTP/1.1
Security
TLS 1.2, RSA, AES_256_GCM
Server
69.173.144.138 , Germany, ASN26667 (RUBICONPROJECT - Magnite, Inc., US),
Reverse DNS
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://c1.adform.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

Expires
0
Cache-Control
no-cache,no-store,must-revalidate
P3P
CP="NOI CURa ADMa DEVa TAIa OUR BUS IND UNI COM NAV INT"
X-RPHost
657c4847ba21a5374ddc9f658a799ec4
Pragma
no-cache
GET
H2
200
tpui
ih.adscale.de/adscale-ih/ Frame 2542
0
59 B
253ms
119ms
Image
text/plain
18.157.227.77
Amazon.com
General
Full URL
https://ih.adscale.de/adscale-ih/tpui?tpid=42&tpuid=5351721985196806187&cburl=https%3a%2f%2fc1.adform.net%2fserving%2fcookie%2fmatch%3fparty%3d9%26uid%3D__ADSCALE_USER_ID__
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
18.157.227.77 Frankfurt am Main, Germany, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-18-157-227-77.eu-central-1.compute.amazonaws.com
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://c1.adform.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
text/plain; charset=UTF-8
content-length
0
GET
H2
200
/
rtb-csync.smartadserver.com/redir/ Frame 2542
43 B
113 B
59ms
56ms
Image
image/gif
81.17.55.173
LEASEWEB-NL-AMS-0...
General
Full URL
https://rtb-csync.smartadserver.com/redir/?partnerid=22&partneruserid=5351721985196806187&redirurl=https%3a%2f%2fc1.adform.net%2fserving%2fcookie%2fmatch%3fparty%3d10%26cid%3DSMART_USER_ID
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
81.17.55.173 , Netherlands, ASN60781 (LEASEWEB-NL-AMS-01 LeaseWeb Netherlands B.V., NL),
Reverse DNS
Software
/
Resource Hash
89fe0ee6020314794fc2cfeacf3d10c31050cfe56f8ebddf1ed0a33fbe941fa7

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://c1.adform.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

date
Wed, 16 Sep 2026 06:45:46 GMT
content-type
image/gif
GET
H/1.1
200
OK
u
user-sync.fwmrm.net/ad/ Frame 2542
43 B
504 B
241ms
84ms
Image
image/gif
18.134.84.75
Amazon.com
General
Full URL
https://user-sync.fwmrm.net/ad/u?mode=user-register&dspid=55&dspuid=5351721985196806187
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_128_GCM
Server
18.134.84.75 City of London, United Kingdom, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-18-134-84-75.eu-west-2.compute.amazonaws.com
Software
/
Resource Hash
2ddeade3a8991666b89f2a0c3aaba4508852838488781e260d45bc886f1172a5

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://c1.adform.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

Cache-Control
no-store
Pragma
no-cache
Connection
keep-alive
Expires
0
X-Fw-Request-Id
uml27f2_1789541147331017682
Content-Length
43
Keep-Alive
timeout=300
Date
Wed, 16 Sep 2026 06:45:47 GMT
P3P
policyref="https://www.freewheel.tv/w3c/p3p.xml",CP="ALL DSP COR NID"
Content-Type
image/gif
GET
H2
200
sync
x.bidswitch.net/ Frame 2542
43 B
164 B
251ms
80ms
Image
image/gif
35.214.136.108
Google LLC
General
Full URL
https://x.bidswitch.net/sync?dsp_id=70&user_id=5351721985196806187
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
35.214.136.108 Groningen, Netherlands, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
108.136.214.35.bc.googleusercontent.com
Software
/
Resource Hash
548f2d6f4d0d820c6c5ffbeffcbd7f0e73193e2932eefe542accc84762deec87

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://c1.adform.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

via
1.1 google
cache-control
no-cache, no-store, must-revalidate
alt-svc
h3=":443"; ma=2592000
content-length
43
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
image/gif
GET
H3
200
rum
dsum-sec.casalemedia.com/ Frame 2542
43 B
748 B
61ms
59ms
Image
image/gif
104.18.27.193
Cloudflare
General
Full URL
https://dsum-sec.casalemedia.com/rum?cm_dsp_id=111&external_user_id=5351721985196806187&expiration=1790750747
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.18.27.193 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
b1442e85b03bdcaf66dc58c7abb98745dd2687d86350be9a298a1d9382ac849b

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://c1.adform.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache
nel
{"report_to":"cf-nel","success_fraction":0.01,"max_age":604800}
cf-cache-status
DYNAMIC
pragma
no-cache
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=PXwSwbdP%2B885TdfxP6OWcOwW2vOGsHF3aqntrOGJEq0fTtcs3g%2FxtncH7A4qLbj2UVwGWw%2FQMXBJSQtlrBF%2FVKOeWfuNVRe3%2B%2B7YowFPlBbZChhqlYRTMbkj0%2B7GA3MQR4c5buAYCRNCEA%3D%3D"}]}
cf-ray
a3bde90928c6bf60-WAW
expires
0
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
content-length
43
p3p
policyref="/w3c/p3p.xml", CP="NOI DSP COR DEVa TAIa OUR BUS UNI"
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
image/gif
server
cloudflare
priority
u=3,i
GET
H/1.1
200
OK
info2
uipglob.semasio.net/adform/1/ Frame 2542
Redirect Chain
  • https://uipglob.semasio.net/adform/1/info?sType=sync&sExtCookieId=5351721985196806187&sInitiator=external
  • https://uipglob.semasio.net/adform/1/info2?sType=sync&sExtCookieId=5351721985196806187&sInitiator=external
42 B
603 B
71ms
71ms
Image
image/gif
77.243.51.121
NETIC-AS Netic A/S
General
Full URL
https://uipglob.semasio.net/adform/1/info2?sType=sync&sExtCookieId=5351721985196806187&sInitiator=external
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
HTTP/1.1
Server
77.243.51.121 Aalborg Øst, Denmark, ASN42697 (NETIC-AS Netic A/S, DK),
Reverse DNS
Software
/
Resource Hash
99c2917ee5b2a01459a923bdd1c676f15ee73b62b87f696e6735312d26f51e12

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer
https://c1.adform.net/

Response headers

cache-control
no-store, no-cache, must-revalidate, post-check=0, pre-check=0
routing-server-id
-1
frontend-id
7
pragma
no-cache
expires
Sat, 01 Jan 2011 12:00:00 GMT
access-control-allow-origin
*
uip-response-status
Ok
p3p
policyref="http://uip.semasio.net/w3c/p3p.xml", CP="NOI PSAa PSDa OUR IND UNI CNT"
date
Wed, 16 Sep 2026 06:45:47 GMT
content-length
42
content-type
image/gif

Redirect headers

cache-control
no-store, no-cache, must-revalidate, post-check=0, pre-check=0
location
/adform/1/info2?sType=sync&sExtCookieId=5351721985196806187&sInitiator=external
routing-server-id
-1
frontend-id
11
pragma
no-cache
expires
Sat, 01 Jan 2011 12:00:00 GMT
access-control-allow-origin
*
uip-response-status
Ok
p3p
policyref="http://uip.semasio.net/w3c/p3p.xml", CP="NOI PSAa PSDa OUR IND UNI CNT"
date
Wed, 16 Sep 2026 06:45:47 GMT
content-length
0
GET
H/1.1
200
OK
match
ps.eyeota.net/ Frame 2542
0
354 B
253ms
119ms
Image
text/plain
63.183.69.9
Amazon.com
General
Full URL
https://ps.eyeota.net/match?uid=5351721985196806187&bid=9gdtmu1
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_256_GCM
Server
63.183.69.9 Frankfurt am Main, Germany, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-63-183-69-9.eu-central-1.compute.amazonaws.com
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://c1.adform.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-length
0
date
Wed, 16 Sep 2026 06:45:47 GMT
p3p
CP="CURa ADMa DEVa TAIo PSAo PSDo OUR SAMo BUS UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR", policyref="http://ps.eyeota.net/w3c/p3p.xml"
GET
H2
204
/
loadm.exelator.com/load/ Frame 2542
0
325 B
366ms
137ms
Image
text/plain
34.242.143.121
Amazon.com
General
Full URL
https://loadm.exelator.com/load/?p=204&g=710&j=0&buid=5351721985196806187
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
34.242.143.121 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-34-242-143-121.eu-west-1.compute.amazonaws.com
Software
nginx / Undertow/1
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://c1.adform.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache
p3p
policyref=/w3c/p3p.xml, CP=NOI DSP COR NID CURa ADMa DEVa PSAa PSDa OUR BUS COM INT OTC PUR STA, policyref=/w3c/p3p.xml, CP=NOI DSP COR NID CURa ADMa DEVa PSAa PSDa OUR BUS COM INT OTC PUR STA
date
Wed, 16 Sep 2026 06:45:47 GMT
x-powered-by
Undertow/1
server
nginx
access-control-allow-credentials
true
GET
H2
200
generic
match.adsrvr.org/track/cmf/ Frame 2542
Redirect Chain
  • https://idsync.rlcdn.com/398366.gif?partner_uid=5351721985196806187
  • https://idsync.rlcdn.com/1000.gif?memo=CJ6oGBIeChoIARCUdRoTNTM1MTcyMTk4NTE5NjgwNjE4NxAAGg0Im_ao1QYSBQjoBxAAQgBKAA
  • https://match.adsrvr.org/track/cmf/generic?ttd_pid=liveramp&ttd_tpi=1
70 B
148 B
72ms
71ms
Image
image/gif
15.197.193.217
Amazon.com
General
Full URL
https://match.adsrvr.org/track/cmf/generic?ttd_pid=liveramp&ttd_tpi=1
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
H2
Server
15.197.193.217 Seattle, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
a12b7a488abeaa9e4.awsglobalaccelerator.com
Software
Kestrel /
Resource Hash
8d70b3e6badb6973663b398d297bb32eaedd08826a1af98d0a1cfce5324ffce0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer
https://c1.adform.net/

Response headers

content-length
70
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
image/gif
server
Kestrel

Redirect headers

cache-control
no-cache, no-store
timing-allow-origin
*
location
https://match.adsrvr.org/track/cmf/generic?ttd_pid=liveramp&ttd_tpi=1
via
1.1 google
alt-svc
h3=":443"; ma=2592000
p3p
CP="NOI DSP COR NID CURa ADMa DEVa PSAa PSDa OUR BUS COM INT OTC PUR STA"
content-length
0
date
Wed, 16 Sep 2026 06:45:47 GMT
GET
H2
404
qmap
sync.crwdcntrl.net/ Frame 2542
49 B
268 B
293ms
131ms
Image
image/gif
34.254.69.83
Amazon.com
General
Full URL
https://sync.crwdcntrl.net/qmap?c=6466&tp=ADFM&tpid=5351721985196806187
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
34.254.69.83 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-34-254-69-83.eu-west-1.compute.amazonaws.com
Software
/
Resource Hash
2f561b02a49376e3679acd5975e3790abdff09ecbadfa1e1858c7ba26e3ffcef
Security Headers
Name Value
Strict-Transport-Security max-age=31536000 ; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://c1.adform.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000 ; includeSubDomains
cache-control
no-cache
pragma
no-cache
expires
0
access-control-allow-origin
*
p3p
CP=NOI DSP COR NID PSAa PSDa OUR UNI COM NAV
content-length
49
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
image/gif
GET
H2
200
sd
eu-u.openx.net/w/1.0/ Frame 2542
43 B
278 B
151ms
57ms
Image
image/gif
35.244.159.8
Google LLC
General
Full URL
https://eu-u.openx.net/w/1.0/sd?id=537113484&val=5351721985196806187
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
35.244.159.8 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
8.159.244.35.bc.googleusercontent.com
Software
/
Resource Hash
4e0705327480ad2323cb03d9c450ffcae4a98bf3a5382fa0c7882145ed620e49

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://c1.adform.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
private, max-age=0, no-cache
pragma
no-cache
x-forwarded-for
79.127.186.227
via
1.1 google
expires
Mon, 26 Jul 1997 05:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
43
p3p
CP="CUR ADM OUR NOR STA NID"
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
image/gif
vary
Accept
GET
H/1.1
200
OK
/
cm.adsafety.net/ Frame 2542
43 B
229 B
255ms
119ms
Image
image/gif
193.135.9.133
IP-PROJECTS Micha...
General
Full URL
https://cm.adsafety.net/?_cmsrc=adformx&idt=100&did=5351721985196806187
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
HTTP/1.1
Security
TLS 1.2, ECDHE_ECDSA, AES_128_GCM
Server
193.135.9.133 , Germany, ASN48314 (IP-PROJECTS Michael Sebastian Schinzel trading as IP-Projects GmbH & Co. KG, DE),
Reverse DNS
Software
nginx /
Resource Hash
cf4724b2f736ed1a0ae6bc28f1ead963d9cd2c1fd87b6ef32e7799fc1c5c8bda

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://c1.adform.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

Content-Length
43
Date
Wed, 16 Sep 2026 06:45:47 GMT
Content-Type
image/gif
Last-Modified
Mon, 28 Sep 1970 06:00:00 GMT
Server
nginx
Connection
keep-alive
GET
H2
200
/
c1.adform.net/serving/cookie/match/ Frame 2542
Redirect Chain
  • https://cm.g.doubleclick.net/pixel?google_nid=1024&google_cm&google_ula=1641347&party=1&google_hm=NTM1MTcyMTk4NTE5NjgwNjE4Nw&process_consent=T
  • https://c1.adform.net/serving/cookie/match/?party=1&google_gid=CAESEAuus1h_iTVn7AlW2yPNDwU&google_cver=1&google_ula=1641347,0
35 B
600 B
104ms
103ms
Image
image/gif
37.157.2.13
ADFORM Adform A/S
General
Full URL
https://c1.adform.net/serving/cookie/match/?party=1&google_gid=CAESEAuus1h_iTVn7AlW2yPNDwU&google_cver=1&google_ula=1641347,0
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
H2
Server
37.157.2.13 , Denmark, ASN198622 (ADFORM Adform A/S, DK),
Reverse DNS
Software
nginx /
Resource Hash
8337212354871836e6763a41e615916c89bac5b3f1f0adf60ba43c7c806e1015
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer
https://c1.adform.net/

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
access-control-max-age
86400
cache-control
no-cache, no-store, must-revalidate, no-transform
pragma
no-cache
accept-ch
Sec-CH-UA,Sec-CH-UA-Arch,Sec-CH-UA-Bitness,Sec-CH-UA-Full-Version-List,Sec-CH-UA-Mobile,Sec-CH-UA-Model,Sec-CH-UA-Platform,Sec-CH-UA-Platform-Version
access-control-allow-credentials
true
access-control-allow-methods
GET
expires
-1
access-control-allow-origin
*
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
image/gif
server
nginx
access-control-allow-headers
Content-Type,Cache-Control,Accept-Encoding,X-Requested-With

Redirect headers

cache-control
no-cache, must-revalidate
location
https://c1.adform.net/serving/cookie/match/?party=1&google_gid=CAESEAuus1h_iTVn7AlW2yPNDwU&google_cver=1&google_ula=1641347,0
pragma
no-cache
cross-origin-resource-policy
cross-origin
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
content-length
334
date
Wed, 16 Sep 2026 06:45:47 GMT
x-xss-protection
0
content-type
text/html; charset=UTF-8
server
HTTP server (unknown)
GET

getuid
secure.adnxs.com/ Frame 2542
0
0


GET
H2
200
Pug
simage2.pubmatic.com/AdServer/ Frame 2542
0
75 B
62ms
47ms
Image
text/html
103.231.98.109
PubMatic
General
Full URL
https://simage2.pubmatic.com/AdServer/Pug?vcode=bz0yJnR5cGU9MSZjb2RlPTI4NzUmdGw9NDMyMDA=&piggybackCookie=5351721985196806187
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
103.231.98.109 , Japan, ASN62713 (AS-PUBMATIC - PubMatic, Inc., US),
Reverse DNS
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=16070400; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://c1.adform.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=16070400; includeSubDomains
cache-control
no-store, no-cache, private
p3p
CP="NOI DSP COR LAW CUR ADMo DEVo TAIo PSAo PSDo IVAo IVDo HISo OTPo OUR SAMo BUS UNI COM NAV INT DEM CNT STA PRE LOC"
content-encoding
gzip
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
text/html; charset=utf-8
server
nginx
GET
H2
200
plf
c1.adform.net/imatch/ Frame 2542
0
384 B
137ms
135ms
Image
text/plain
37.157.2.13
ADFORM Adform A/S
General
Full URL
https://c1.adform.net/imatch/plf?name=plfm
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
37.157.2.13 , Denmark, ASN198622 (ADFORM Adform A/S, DK),
Reverse DNS
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
access-control-max-age
86400
accept-ch
Sec-CH-UA,Sec-CH-UA-Arch,Sec-CH-UA-Bitness,Sec-CH-UA-Full-Version-List,Sec-CH-UA-Mobile,Sec-CH-UA-Model,Sec-CH-UA-Platform,Sec-CH-UA-Platform-Version
access-control-allow-credentials
true
access-control-allow-methods
GET
access-control-allow-origin
*
date
Wed, 16 Sep 2026 06:45:47 GMT
server
nginx
access-control-allow-headers
Content-Type,Cache-Control,Accept-Encoding,X-Requested-With
GET
H/1.1
200
OK
cs
pdw-adf.userreport.com/ Frame 2542
43 B
445 B
274ms
121ms
Image
image/gif
99.84.152.34
Amazon.com
General
Full URL
https://pdw-adf.userreport.com/cs
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_128_GCM
Server
99.84.152.34 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-99-84-152-34.fra56.r.cloudfront.net
Software
nginx/1.24.0 /
Resource Hash
cf4724b2f736ed1a0ae6bc28f1ead963d9cd2c1fd87b6ef32e7799fc1c5c8bda

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://c1.adform.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

Age
16695
Connection
keep-alive
Via
1.1 72ef5472ad44eb2052cf834a07235dd8.cloudfront.net (CloudFront)
X-Cache
Hit from cloudfront
Content-Length
43
X-Amz-Cf-Id
ASBIK_X97D8yPHAoZbQIYZGBQB6dkUAZsjUPp1wSRc-HBFS5FnfMAg==
Date
Wed, 16 Sep 2026 02:07:32 GMT
Content-Type
image/gif
Last-Modified
Mon, 28 Sep 1970 06:00:00 GMT
Server
nginx/1.24.0
X-Amz-Cf-Pop
FRA56-P13
GET
H3
200
p
a.audrte.com/ Frame 2542
Redirect Chain
  • https://a.audrte.com/a?adform_uid=5351721985196806187
  • https://cm.g.doubleclick.net/pixel?google_nid=ar101281&google_hm=bXUzcWxlZXIteHVUYmhaT2pRZmlmUWFhblRvVzJhZy1hZA%3D%3D&gdpr=0&gdpr_consent=&google_redir=https%3A%2F%2Fa.audrte.com%2Fddp%3Fred%3DeyJ1...
  • https://a.audrte.com/ddp?red=eyJ1IjoiaHR0cHM6Ly9hLmF1ZHJ0ZS5jb206NDQzL3AiLCJkIjpbXX0%3D&aruid=mu3qleer-xuTbhZOjQfifQaanToW2ag-ad&gdpr=0&gdpr_consent=
  • https://a.audrte.com/p
68 B
89 B
64ms
64ms
Image
image/png
34.102.136.131
Google LLC
General
Full URL
https://a.audrte.com/p
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
H3
Server
34.102.136.131 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
131.136.102.34.bc.googleusercontent.com
Software
Google Frontend /
Resource Hash
2aa4fa20701cdd6d8d56046069001186b5267e3ee7d0ef618ad2f4a683723e11

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer
https://c1.adform.net/

Response headers

access-control-allow-credentials
true
access-control-allow-methods
POST, GET, OPTIONS
via
1.1 google
access-control-allow-origin
*
alt-svc
h3=":443"; ma=2592000
content-length
68
date
Wed, 16 Sep 2026 06:45:47 GMT
x-cloud-trace-context
85547d790c04aeee60dc471c146c9c16
content-type
image/png
vary
Origin, Access-Control-Request-Method, Access-Control-Request-Headers
server
Google Frontend

Redirect headers

location
https://a.audrte.com:443/p
access-control-allow-credentials
true
access-control-allow-methods
POST, GET, OPTIONS
via
1.1 google
access-control-allow-origin
*
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
0
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
text/html
x-cloud-trace-context
b26773a46bf49cddfc95973877bffc5e
vary
Origin, Access-Control-Request-Method, Access-Control-Request-Headers
server
Google Frontend
GET
H2
200
match
c1.adform.net/serving/cookie/ Frame 2542
Redirect Chain
  • https://dpm.demdex.net/ibs:dpid=1586&dpuuid=5351721985196806187&redir=https%3a%2f%2fc1.adform.net%2fserving%2fcookie%2fmatch%3fparty%3d1007%26cid%3D%24%7BDD_UUID%7D%26noredirect%3D1
  • https://dpm.demdex.net/demconf.jpg?et:ibs%7cdata:dpid=1586&dpuuid=5351721985196806187&redir=https%3a%2f%2fc1.adform.net%2fserving%2fcookie%2fmatch%3fparty%3d1007%26cid%3D%24%7BDD_UUID%7D%26noredire...
  • https://c1.adform.net/serving/cookie/match?party=1007&cid=05182160400965987825571395172295940782&noredirect=1
35 B
600 B
110ms
110ms
Image
image/gif
37.157.2.13
ADFORM Adform A/S
General
Full URL
https://c1.adform.net/serving/cookie/match?party=1007&cid=05182160400965987825571395172295940782&noredirect=1
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
H2
Server
37.157.2.13 , Denmark, ASN198622 (ADFORM Adform A/S, DK),
Reverse DNS
Software
nginx /
Resource Hash
8337212354871836e6763a41e615916c89bac5b3f1f0adf60ba43c7c806e1015
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer
https://c1.adform.net/

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
access-control-max-age
86400
cache-control
no-cache, no-store, must-revalidate, no-transform
pragma
no-cache
accept-ch
Sec-CH-UA,Sec-CH-UA-Arch,Sec-CH-UA-Bitness,Sec-CH-UA-Full-Version-List,Sec-CH-UA-Mobile,Sec-CH-UA-Model,Sec-CH-UA-Platform,Sec-CH-UA-Platform-Version
access-control-allow-credentials
true
access-control-allow-methods
GET
expires
-1
access-control-allow-origin
*
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
image/gif
server
nginx
access-control-allow-headers
Content-Type,Cache-Control,Accept-Encoding,X-Requested-With

Redirect headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
no-cache,no-store,must-revalidate,max-age=0,proxy-revalidate,no-transform,private
location
https://c1.adform.net/serving/cookie/match?party=1007&cid=05182160400965987825571395172295940782&noredirect=1
dcs
dcs-prod-irl1-1-v094-0fc09c4b4.edge-irl1.demdex.com 3 ms
pragma
no-cache
x-tid
HGBExtaq3bs=
expires
Thu, 01 Jan 1970 00:00:00 UTC
content-length
0
p3p
policyref="/w3c/p3p.xml", CP="NOI NID CURa ADMa DEVa PSAa PSDa OUR SAMa BUS PUR COM NAV INT"
date
Wed, 16 Sep 2026 06:45:47 GMT
GET
H2
200
g.pixel
aa.agkn.com/adscores/ Frame 2542
0
307 B
894ms
446ms
Image
text/plain
35.167.241.13
Amazon.com
General
Full URL
https://aa.agkn.com/adscores/g.pixel?sid=9212269628&_puid=5351721985196806187
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
35.167.241.13 Boardman, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-35-167-241-13.us-west-2.compute.amazonaws.com
Software
AAWebServer /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://c1.adform.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, no-store, must-revalidate
pragma
no-cache
access-control-allow-methods
GET, OPTIONS
expires
0
access-control-allow-origin
*
p3p
policyref="https://www.agkn.com/p3p/p3p.xml",CP="NOI NID"
date
Wed, 16 Sep 2026 06:45:47 GMT
server
AAWebServer
access-control-allow-headers
accept, cache-control, origin, x-requested-with, x-file-name, content-type
GET
H/1.1
200
OK
/
dsp.adfarm1.adition.com/cookie/ Frame 2542
0
235 B
273ms
124ms
Image
text/plain
85.114.159.93
MYLOC-AS WIIT AG
General
Full URL
https://dsp.adfarm1.adition.com/cookie/?redirect=https%3A%2F%2Fc1.adform.net%2Fserving%2Fcookie%2Fmatch%2F%3Fparty%3D1049%26cid%3D%25%25COOKIE%25%25
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
HTTP/1.1
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
85.114.159.93 , Germany, ASN24961 (MYLOC-AS WIIT AG, DE),
Reverse DNS
dsp.adfarm1.adition.com
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://c1.adform.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

Content-Length
0
p3p
policyref="http://imagesrv.adition.com/w3c/p3p.xml",CP="NON DSP ADM DEV PSD IVDo OTPi OUR IND STP PHY PRE NAV UNI"
Date
Wed, 16 Sep 2026 06:45:47 GMT
Server
nginx
Connection
keep-alive
GET
H2
200
match
c1.adform.net/serving/cookie/ Frame 2542
Redirect Chain
  • https://pm.w55c.net/ping_match.gif?st=adform&rurl=https%3a%2f%2fc1.adform.net%2fserving%2fcookie%2fmatch%3fparty%3d1084%26cid%3D_wfivefivec_
  • https://pm.w55c.net/ping_match.gif?scc=1&st=adform&rurl=https%3A%2F%2Fc1.adform.net%2Fserving%2Fcookie%2Fmatch%3Fparty%3D1084%26cid%3D_wfivefivec_
  • https://c1.adform.net/serving/cookie/match?party=1084&cid=F1ff0hWD1X6JoT5
35 B
591 B
71ms
71ms
Image
image/gif
37.157.2.13
ADFORM Adform A/S
General
Full URL
https://c1.adform.net/serving/cookie/match?party=1084&cid=F1ff0hWD1X6JoT5
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
H2
Server
37.157.2.13 , Denmark, ASN198622 (ADFORM Adform A/S, DK),
Reverse DNS
Software
nginx /
Resource Hash
8337212354871836e6763a41e615916c89bac5b3f1f0adf60ba43c7c806e1015
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer
https://c1.adform.net/

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
access-control-max-age
86400
cache-control
no-cache, no-store, must-revalidate, no-transform
pragma
no-cache
accept-ch
Sec-CH-UA,Sec-CH-UA-Arch,Sec-CH-UA-Bitness,Sec-CH-UA-Full-Version-List,Sec-CH-UA-Mobile,Sec-CH-UA-Model,Sec-CH-UA-Platform,Sec-CH-UA-Platform-Version
access-control-allow-credentials
true
access-control-allow-methods
GET
expires
-1
access-control-allow-origin
*
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
image/gif
server
nginx
access-control-allow-headers
Content-Type,Cache-Control,Accept-Encoding,X-Requested-With

Redirect headers

strict-transport-security
max-age=2592000; includeSubDomains
cache-control
no-cache, must-revalidate
location
https://c1.adform.net/serving/cookie/match?party=1084&cid=F1ff0hWD1X6JoT5
pragma
no-cache
via
1.1 google
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000
content-length
0
date
Wed, 16 Sep 2026 06:45:46 GMT
server
PingMatch/v2.0.30-837-g97d465c#main edge-prod-euw1-53vk@europe-west1
GET
H2
200
generic
match.adsrvr.org/track/cmf/ Frame 2542
70 B
149 B
312ms
135ms
Image
image/gif
15.197.193.217
Amazon.com
General
Full URL
https://match.adsrvr.org/track/cmf/generic?ttd_pid=71ei9rr&ttd_tpi=1
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
15.197.193.217 Seattle, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
a12b7a488abeaa9e4.awsglobalaccelerator.com
Software
Kestrel /
Resource Hash
8d70b3e6badb6973663b398d297bb32eaedd08826a1af98d0a1cfce5324ffce0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://c1.adform.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-length
70
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
image/gif
server
Kestrel
GET
H2
200
0.gif
id5-sync.com/s/10/ Frame 2542
43 B
1 KB
243ms
98ms
Image
image/gif
135.125.170.28
OVH OVH SAS
General
Full URL
https://id5-sync.com/s/10/0.gif?puid=5351721985196806187
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
135.125.170.28 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
ns31872155.ip-135-125-170.eu
Software
/
Resource Hash
a065920df8cc4016d67c3a464be90099c9d28ffe7c9e6ee3a18f257efc58cbd7
Security Headers
Name Value
Strict-Transport-Security max-age=63072000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://c1.adform.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=63072000; includeSubDomains; preload
p3p
CP="CAO PSA OUR"
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
image/gif;charset=UTF-8
vary
Origin, Access-Control-Request-Method, Access-Control-Request-Headers
GET
H2
200
/
c1.adform.net/serving/cookie/match/ Frame 2542
Redirect Chain
  • https://redirect.frontend.weborama.fr/redirect/standard?url=https%3A%2F%2Fc1.adform.net%2Fserving%2Fcookie%2Fmatch%2F%3Fparty%3D1145%26cid%3D%7BWEBO_CID%7D
  • https://redirect.frontend.weborama.fr/redirect/standard?url=https%3A%2F%2Fc1.adform.net%2Fserving%2Fcookie%2Fmatch%2F%3Fparty%3D1145%26cid%3D%7BWEBO_CID%7D&bounce=1&random=3172369169
  • https://c1.adform.net/serving/cookie/match/?party=1145&cid=7s6MGZXi8VEvDEk4DMJY5e
35 B
600 B
104ms
104ms
Image
image/gif
37.157.2.13
ADFORM Adform A/S
General
Full URL
https://c1.adform.net/serving/cookie/match/?party=1145&cid=7s6MGZXi8VEvDEk4DMJY5e
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
H2
Server
37.157.2.13 , Denmark, ASN198622 (ADFORM Adform A/S, DK),
Reverse DNS
Software
nginx /
Resource Hash
8337212354871836e6763a41e615916c89bac5b3f1f0adf60ba43c7c806e1015
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer
https://c1.adform.net/

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
access-control-max-age
86400
cache-control
no-cache, no-store, must-revalidate, no-transform
pragma
no-cache
accept-ch
Sec-CH-UA,Sec-CH-UA-Arch,Sec-CH-UA-Bitness,Sec-CH-UA-Full-Version-List,Sec-CH-UA-Mobile,Sec-CH-UA-Model,Sec-CH-UA-Platform,Sec-CH-UA-Platform-Version
access-control-allow-credentials
true
access-control-allow-methods
GET
expires
-1
access-control-allow-origin
*
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
image/gif
server
nginx
access-control-allow-headers
Content-Type,Cache-Control,Accept-Encoding,X-Requested-With

Redirect headers

strict-transport-security
max-age=31536000; includeSubdomains; preload
cache-control
no-store, no-cache, must-revalidate, max-age=0, post-check=0, pre-check=0
location
https://c1.adform.net/serving/cookie/match/?party=1145&cid=7s6MGZXi8VEvDEk4DMJY5e
pragma
no-cache
x-content-type-options
nosniff
referrer-policy
no-referrer-when-downgrade
expires
Tue, 03 Jul 2001 06:00:00 GMT
access-control-allow-origin
*
content-length
0
p3p
CP="NOI DSP COR CURa DEVa PSAa OUR STP UNI DEM"
date
Wed, 16 Sep 2026 06:45:47 GMT
last-modified
Wed, 16 Sep 2026 06:45:47 GMT
vary
Origin
x-frame-options
SAMEORIGIN
GET
H2
200
um
sync.teads.tv/ Frame 2542
23 B
276 B
221ms
95ms
Image
image/gif
151.101.66.132
Fastly
General
Full URL
https://sync.teads.tv/um?eid=119&uid=5351721985196806187
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
151.101.66.132 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
pekko-http/1.1.0 /
Resource Hash
328e90a318268aea96180cc31666ae6d6f79d90d078c123bc3d98ee08a192fb7

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://c1.adform.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-user-geo
EU-WEST-1
cache-control
max-age=0, no-cache, no-store
x-timer
S1789541147.224816,VS0,VE35
x-check-cacheable
NO
via
1.1 varnish
accept-ranges
bytes
x-cache
MISS
content-length
23
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
image/gif
x-served-by
cache-vie6352-VIE
server
pekko-http/1.1.0
x-cache-hits
0
traffic-path
DUBDC2, VIE, Europe
GET
H2
204
/
s.ad.smaato.net/c/ Frame 2542
0
66 B
254ms
108ms
Image
text/plain
35.214.217.206
Google LLC
General
Full URL
https://s.ad.smaato.net/c/?dspInit=1067&dspCookie=5351721985196806187
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
35.214.217.206 Groningen, Netherlands, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
206.217.214.35.bc.googleusercontent.com
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://c1.adform.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

via
1.1 google
date
Wed, 16 Sep 2026 06:45:46 GMT
cache-control
no-cache, must-revalidate
GET

5351721985196806187
match.contentexchange.me/adform/ Frame 2542
0
0


GET
H2
200
set_user_agent_id_mapping
cookie-matching.mediarithmics.com/v1/ Frame 2542
70 B
180 B
277ms
126ms
Image
image/png
54.36.150.186
OVH OVH SAS
General
Full URL
https://cookie-matching.mediarithmics.com/v1/set_user_agent_id_mapping?dom_token=adform25&identifier=5351721985196806187
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
54.36.150.186 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
ip186.ip-54-36-150.eu
Software
/
Resource Hash
f3ca3118d9eceb4028fb8b62693e34913badaedfc8d62eed83ed744697bf12f9
Security Headers
Name Value
Strict-Transport-Security max-age=63072000;includeSubDomains;preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://c1.adform.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=63072000;includeSubDomains;preload
content-length
70
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
image/png
GET
H/1.1
200
OK
/
pixel.onaudience.com/ Frame 2542
35 B
99 B
181ms
59ms
Image
image/gif
79.137.99.232
OVH OVH SAS
General
Full URL
https://pixel.onaudience.com/?mapped=5351721985196806187&partner=68
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_128_GCM
Server
79.137.99.232 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
ns3239897.ip-79-137-99.eu
Software
/
Resource Hash
6adc3d4c1056996e4e8b765a62604c78b1f867cceb3b15d0b9bedb7c4857f992

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://c1.adform.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-type
image/gif
content-length
35
GET
H2
200
xuid
eb2.3lift.com/ Frame 2542
37 B
140 B
256ms
119ms
Image
image/gif
3.120.74.76
Amazon.com
General
Full URL
https://eb2.3lift.com/xuid?mid=7354&xuid=5351721985196806187&dongle=AD20
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.120.74.76 Frankfurt am Main, Germany, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-3-120-74-76.eu-central-1.compute.amazonaws.com
Software
/
Resource Hash
bb229a48bee31f5d54ca12dc9bd960c63a671f0d4be86a054c1d324a44499d96

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://c1.adform.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, no-store, must-revalidate
content-length
37
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
image/gif
GET
H/1.1
200
OK
/
pixel.onaudience.com/ Frame 2542
35 B
99 B
239ms
123ms
Image
image/gif
79.137.99.232
OVH OVH SAS
General
Full URL
https://pixel.onaudience.com/?partner=290&mapped=5351721985196806187
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_128_GCM
Server
79.137.99.232 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
ns3239897.ip-79-137-99.eu
Software
/
Resource Hash
6adc3d4c1056996e4e8b765a62604c78b1f867cceb3b15d0b9bedb7c4857f992

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://c1.adform.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-type
image/gif
content-length
35
GET
H2
200
/
onetag-sys.com/match/ Frame 2542
0
183 B
253ms
126ms
Image
text/plain
46.105.34.150
OVH OVH SAS
General
Full URL
https://onetag-sys.com/match/?int_id=220&uid=5351721985196806187
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
46.105.34.150 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
ip150.ip-46-105-34.eu
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=15552000

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://c1.adform.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=15552000
cache-control
no-transform, no-cache
content-length
0
p3p
CP='CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR'
date
Wed, 16 Sep 2026 06:45:47 GMT
GET
H2
200
plf
c1.adform.net/imatch/ Frame 2542
0
384 B
135ms
134ms
Image
text/plain
37.157.2.13
ADFORM Adform A/S
General
Full URL
https://c1.adform.net/imatch/plf?name=plfl
Requested by
Host: c1.adform.net
URL: https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
37.157.2.13 , Denmark, ASN198622 (ADFORM Adform A/S, DK),
Reverse DNS
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://c1.adform.net/imatch/pixels?bt=0&uid=5351721985196806187&agencyId=3265&advertiserId=2147056&src=tp&rnd=747817
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
access-control-max-age
86400
accept-ch
Sec-CH-UA,Sec-CH-UA-Arch,Sec-CH-UA-Bitness,Sec-CH-UA-Full-Version-List,Sec-CH-UA-Mobile,Sec-CH-UA-Model,Sec-CH-UA-Platform,Sec-CH-UA-Platform-Version
access-control-allow-credentials
true
access-control-allow-methods
GET
access-control-allow-origin
*
date
Wed, 16 Sep 2026 06:45:47 GMT
server
nginx
access-control-allow-headers
Content-Type,Cache-Control,Accept-Encoding,X-Requested-With
GET
H2
200
perform.php Show response
sv.ciblelink.com/profiling/
965 B
1 KB
278ms
115ms
Script
text/javascript
51.210.24.88
OVH OVH SAS
General
Full URL
https://sv.ciblelink.com/profiling/perform.php?name=&action=Product
Requested by
Host: profiling.veoxa.com
URL: https://profiling.veoxa.com/boot/request/?aid=2764&pid=3539&action=Product&productId=412
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
51.210.24.88 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
ns3257326.ip-51-210-24.eu
Software
nginx/1.24.0 (Ubuntu) /
Resource Hash
d31bc11f551e8d8ca03647fe969ea1e7bb0ec2aa429cb85a4a49935d24ef4b73

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

expires
Sun, 06 Sep 2026 06:45:47 GMT
cache-control
no-store, no-cache, must-revalidate, post-check=0, pre-check=0
date
Wed, 16 Sep 2026 06:45:47 GMT
pragma
no-cache
content-type
text/javascript;charset=UTF-8
server
nginx/1.24.0 (Ubuntu)
POST
H2
200
/ Show response
cognito-identity.eu-west-1.amazonaws.com/
2 KB
2 KB
168ms
168ms
XHR
application/x-amz-json-1.1
52.213.207.85
Amazon.com
General
Full URL
https://cognito-identity.eu-west-1.amazonaws.com/
Requested by
Host: js.smct.io
URL: https://js.smct.io/v7.14.0-beta.20/tag-v7.14.0-beta.20.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
52.213.207.85 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-52-213-207-85.eu-west-1.compute.amazonaws.com
Software
/
Resource Hash
42826ef0ceac082157fa0cda61701c1ee2a77719e550a47c7d3bf504cf7c8b4f
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
X-AMZ-TARGET
AWSCognitoIdentityService.GetCredentialsForIdentity
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
application/x-amz-json-1.1
sec-ch-ua-mobile
?0

Response headers

x-amzn-requestid
85a8e8ef-a7fa-4572-a51a-a3c4b855ac8e
strict-transport-security
max-age=31536000; includeSubDomains
access-control-allow-origin
*
access-control-expose-headers
x-amzn-RequestId,x-amzn-ErrorType,x-amzn-ErrorMessage,Date
content-length
1744
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
application/x-amz-json-1.1
POST
H2
200
/ Show response
cognito-identity.eu-west-1.amazonaws.com/
2 KB
2 KB
91ms
90ms
XHR
application/x-amz-json-1.1
52.213.207.85
Amazon.com
General
Full URL
https://cognito-identity.eu-west-1.amazonaws.com/
Requested by
Host: js.smct.io
URL: https://js.smct.io/v7.14.0-beta.20/tag-v7.14.0-beta.20.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
52.213.207.85 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-52-213-207-85.eu-west-1.compute.amazonaws.com
Software
/
Resource Hash
ad586be2e7f1e25d36fb1bc35e102a0d2a9701807aa3f29815ce5e46f0681949
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
X-AMZ-TARGET
AWSCognitoIdentityService.GetCredentialsForIdentity
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
application/x-amz-json-1.1
sec-ch-ua-mobile
?0

Response headers

x-amzn-requestid
7e627eb9-e43d-48c3-8438-96140eb248bc
strict-transport-security
max-age=31536000; includeSubDomains
access-control-allow-origin
*
access-control-expose-headers
x-amzn-RequestId,x-amzn-ErrorType,x-amzn-ErrorMessage,Date
content-length
1744
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
application/x-amz-json-1.1
POST
H2
204
matomo.php
analytics.queisser.com/
0
38 B
98ms
98ms
Ping
text/html
142.132.237.132
HETZNER-AS Hetzne...
General
Full URL
https://analytics.queisser.com/matomo.php?action_name=Doppelherz%20system%20Kollagen%2011.000%20PLUS%20%7C%2030%20ampu%C5%82ek%20-%20sklep%20Doppelherz&idsite=64&rec=1&r=928610&h=8&m=45&s=46&url=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&_id=c1832cfa1fe065ef&_idn=0&send_image=0&_refts=0&_pkc=Doppelherz%20system&_pkp=122.7&_pks=412&_pkn=Doppelherz%C2%AE%20system%20KOLLAGEN%2011.000%20PLUS%2C%2030%20ampu%C5%82ek%20po%2025ml&pv_id=eLMMzx&pf_net=142&pf_srv=276&pf_tfr=39&pf_dm1=347&uadata=%7B%22formFactors%22%3A%5B%22Desktop%22%5D%2C%22fullVersionList%22%3A%5B%7B%22brand%22%3A%22Chromium%22%2C%22version%22%3A%22153.0.8010.36%22%7D%2C%7B%22brand%22%3A%22Google%20Chrome%22%2C%22version%22%3A%22153.0.8010.36%22%7D%2C%7B%22brand%22%3A%22Not_A%20Brand%22%2C%22version%22%3A%228.0.0.0%22%7D%5D%2C%22mobile%22%3Afalse%2C%22model%22%3A%22%22%2C%22platform%22%3A%22Linux%22%2C%22platformVersion%22%3A%22%22%7D&pdf=1&qt=0&realp=0&wma=0&fla=0&java=0&ag=0&cookie=1&res=1600x1200
Requested by
Host: analytics.queisser.com
URL: https://analytics.queisser.com/matomo.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.132.237.132 Falkenstein, Germany, ASN24940 (HETZNER-AS Hetzner Online GmbH, DE),
Reverse DNS
static.132.237.132.142.clients.your-server.de
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
application/x-www-form-urlencoded; charset=utf-8
sec-ch-ua-mobile
?0

Response headers

access-control-allow-origin
https://sklep.doppelherz.pl
date
Wed, 16 Sep 2026 06:45:47 GMT
content-type
text/html; charset=UTF-8
server
nginx
access-control-allow-credentials
true
POST
H/1.1
200
OK
/ Show response
firehose.eu-west-1.amazonaws.com/
298 B
737 B
122ms
120ms
XHR
application/x-amz-json-1.1
99.80.34.227
Amazon.com
General
Full URL
https://firehose.eu-west-1.amazonaws.com/
Requested by
Host: js.smct.io
URL: https://js.smct.io/v7.14.0-beta.20/tag-v7.14.0-beta.20.js
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_128_GCM
Server
99.80.34.227 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-99-80-34-227.eu-west-1.compute.amazonaws.com
Software
/
Resource Hash
e281dc1a34a238f2ca5e06db4f30a77c173094ed34e4a4bb564d66c100291883

Request headers

sec-ch-ua-platform
"Linux"
Authorization
AWS4-HMAC-SHA256 Credential=ASIAX2DUJRE4XSA65T2W/20260916/eu-west-1/firehose/aws4_request, SignedHeaders=host;x-amz-date;x-amz-security-token;x-amz-target, Signature=9e30bf44f3595b7b2650b2bebf5449962066a4e3f567e7fcfac2ad237d4b6a06
Referer
https://sklep.doppelherz.pl/
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
x-amz-security-token
IQoJb3JpZ2luX2VjEEcaCWV1LXdlc3QtMSJIMEYCIQCRnLtrBiVOQiFDp3ttIjhiG2nv/vUNIl/r+AIUl0YPMgIhAMtk2BIY0TOAghxQm1lPrx2zwmdR0mA0T7jqBOL8W5XFKq8FCBAQBBoMNTM3MTE0ODA2NTg1IgweM9A62g9Py54U8WAqjAWwfxjcV2EKzmH8mdbL2F1klsTcMYvxsaClqHdVT8+LX5oeKzJpuMJoAx8FxBXb2CdbC9z5OWAwC4wKmJrF1WbWb3tkV8N6y23aTZFEHB7U9efdBEiOJtTfdZDQMsbrtfuj5mnC9+Uoyz3JzxHYT5oCoDM4aizuhH7eQ4q06I732YX/IH92ANwoIhH/GXXoWu4t3YZU30h4+oREi9Ln2/Le6j0Ox2To9SEI29u5KCaKV6Rhn6bp4vwFr64u053Pv5DVEp3jb2QonXKKX4HrEUKdvy6wj9YP6NhlivXoAyQdTm5D4//p2uEglJHt7b0Zo8ArC6YoZmWUEtAEEokz0U665MVlpszuSirIvGmzbml3vTLa80IvcNm690gf/nCoe1OuR5DVfq1MKbZPyHaxpFs3b4nF6+suwYyc0sQQKxrtqZID0caHO+AVhmhgrf3aFm18TxBPMg5aWBbP2JKOJdrYhMVY5dGM5N6iyBJVh8NQGiaXvp5DyvVCbEJVO4Iqhxq+HUjOlLYcIbZwQymV4OfDBFP/k1zg8y5ilsb2VvUs/ECPvazMewhY8RMBl4g33tkK45qumBzu4TLML1ytYf1Mbpz8QMVHM214iCRHJTaxbHnqLEmWKFeupdF1rZp6V+oEn3qgjF3R7le+N9xSqZ0roxG0cMELKGdFmAPF3bUI4sZh0gNDesma7SgoZ2uBjDRaqGuaAl6hWtdPHpZ9qEkPzer6y+R3+7FUIcKSW0Yf6xHMdvg3k9PxaY4v/OZYh/6eeSdW4nsNWkk7+cLJKSsBsI40Ei/eu7sF7YffBUy80RsA0Tf5hxy6vbsAYkzo3snIGn78VSm2MFNJuCq1Ze+kkCMJPHIOHfIE5Nq9MJv2qNUGOtwCKEVNh18UuPfz/3SWyIBbB0O5cdZ0b02/4J4Fi8RChtGO1yHyCBeB2zagJ9qu9nWrzC5zCsgdXQ2mHmHIVGnqLLBqcfpB7blbW/Dj+Q0GmrVb0LPlgz0/hYiEY6Vqu+ZHB6T00nBws8VHf1rLRjkk12bBD218a+UXGudWhNco4HHPHlaPPnCgjCl+j9rSPgzI+jcsNsTPieYapvHyhH8jlET8Y/o1uM4BegYjZVhd8vpn+g3FNDevl6SdDS6wHBk4FafjfMprNOFY9YvcZsVYa5aB0dyWTe/u0nMqNjHRPdOD7NAcjaVrhamHegQXtIjlZuSC1IkRzmqL01iRXhj9mr2ackTvWR/7H+zjpDXTItlHr5M7QjPsa50CSVLg0E4kbrXidIN0djzatTq4REATeDT9J/mUgWMFBVmD6hTsAmkJ9xlcOyRMBM0Y/Ix9sbvnCs6L6E0PUVrFoZRm
x-amz-date
20260916T064547Z
x-amz-target
Firehose_20150804.PutRecordBatch
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Content-Type
application/x-amz-json-1.1

Response headers

Access-Control-Expose-Headers
x-amz-request-id,x-amz-id-2,x-amzn-RequestId,x-amzn-ErrorType,x-amzn-ErrorMessage,Date
Content-Encoding
gzip
x-amzn-RequestId
e1aaa84b-8b4f-1d94-828e-9510d175165d
Access-Control-Allow-Origin
*
Content-Length
277
Date
Wed, 16 Sep 2026 06:45:47 GMT
Content-Type
application/x-amz-json-1.1
x-amz-id-2
RXbNHQ2LfbSO/5f0Yw5S2MvLXRz/oKz3CBwZPYuzPsUdgfUAVfodtX7CpjBM6KTpgI15SX4eRQv43nK7+X/2CnLzo9O4t1zf
OPTIONS
H/1.1
200
OK
/
firehose.eu-west-1.amazonaws.com/ Frame
0
0
308ms
137ms
Preflight
99.80.34.227
Amazon.com
General
Full URL
https://firehose.eu-west-1.amazonaws.com/
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_128_GCM
Server
99.80.34.227 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-99-80-34-227.eu-west-1.compute.amazonaws.com
Software
/
Resource Hash

Request headers

Accept
*/*
Access-Control-Request-Headers
authorization,content-type,x-amz-date,x-amz-security-token,x-amz-target
Access-Control-Request-Method
POST
Origin
https://sklep.doppelherz.pl
Sec-Fetch-Mode
cors
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36

Response headers

Access-Control-Allow-Headers
authorization,content-type,x-amz-date,x-amz-security-token,x-amz-target
Access-Control-Allow-Methods
POST
Access-Control-Allow-Origin
*
Access-Control-Expose-Headers
x-amz-request-id,x-amz-id-2,x-amzn-RequestId,x-amzn-ErrorType,x-amzn-ErrorMessage,Date
Access-Control-Max-Age
172800
Content-Encoding
gzip
Content-Length
20
Date
Wed, 16 Sep 2026 06:45:47 GMT
x-amzn-RequestId
d6fd2517-c650-a333-b5d9-184c9c6aa8fa
GET
H2
200
dd.php Show response
sv.ciblelink.com/profiling/
8 B
363 B
102ms
102ms
Script
text/javascript
51.210.24.88
OVH OVH SAS
General
Full URL
https://sv.ciblelink.com/profiling/dd.php?type=Product&boutique=VIDE&category_id=VIDE&produit_id=VIDE&transaction_amount=0&transaction_id=0&refer=https%3A//sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus&refer2=&re=&r=58679245
Requested by
Host: sv.ciblelink.com
URL: https://sv.ciblelink.com/profiling/perform.php?name=&action=Product
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
51.210.24.88 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
ns3257326.ip-51-210-24.eu
Software
nginx/1.24.0 (Ubuntu) /
Resource Hash
45336bf2c27960347588ebaedc466e533d74cb661ed98b7d8b45c27a54e0e596

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

expires
Sun, 06 Sep 2026 06:45:47 GMT
cache-control
no-store, no-cache, must-revalidate, post-check=0, pre-check=0
date
Wed, 16 Sep 2026 06:45:47 GMT
pragma
no-cache
content-type
text/javascript;charset=UTF-8
server
nginx/1.24.0 (Ubuntu)
POST
H/1.1
200
OK
/ Show response
firehose.eu-west-1.amazonaws.com/
299 B
739 B
123ms
122ms
XHR
application/x-amz-json-1.1
99.80.34.227
Amazon.com
General
Full URL
https://firehose.eu-west-1.amazonaws.com/
Requested by
Host: js.smct.io
URL: https://js.smct.io/v7.14.0-beta.20/tag-v7.14.0-beta.20.js
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_128_GCM
Server
99.80.34.227 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-99-80-34-227.eu-west-1.compute.amazonaws.com
Software
/
Resource Hash
56eb6089ee43b1f765a9919693423813fcf856a6068933064c72f5529fd51e54

Request headers

sec-ch-ua-platform
"Linux"
Authorization
AWS4-HMAC-SHA256 Credential=ASIAX2DUJRE4YGKK3LAD/20260916/eu-west-1/firehose/aws4_request, SignedHeaders=host;x-amz-date;x-amz-security-token;x-amz-target, Signature=98fcc467b7f73c2967beecd9021b730871fea1d6650119432e072122ef0b4b17
Referer
https://sklep.doppelherz.pl/
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
x-amz-security-token
IQoJb3JpZ2luX2VjEEcaCWV1LXdlc3QtMSJGMEQCIB113puMDL8jjvK++1+sh41UHbpa0v5tWZeZ5Wb9qp8QAiAjZd+DAtf5Hec3z8v6LYcgqJhsmvJUAt3NFva90wrO1yqvBQgQEAQaDDUzNzExNDgwNjU4NSIM1m5rXuifLzGzHrO2KowFfzko/pax4GipGsLl9Hg3tzxfFYNzvmlebGsVXA8jTWFCw4D+wZ9MNeAqaE8jTsqMSsXRuERoXbnYJovHaS1yjrXz5rgVZqDuxUOMPSZpMIEm09Gbio+7FZp2tOBdR2fOOtG2veM/lqBDh/zsG/Qgr769WneOIXTbeiCYfc+wOeKGVxMJI7JC/oBsYQhMS7GTlrSbwGXUjLJ75xkEDAhuGF7Hv56YBXZCYM08l2vMItKXW0mCjpwjgAVC6qBqGJ6P8RHlC8vHRSWH+Py5igxCeVS+1Qqa+VvoizQrruxTovvqZJdjwRvuoMTex1Eak4YoP4h24V+7bybttfJVNTegDo3h1oNk5xnSIO/yhzGGYbjUDTb6PqLHa/Jypi7jBWa2KiA7k0X9l26EI+hrZTlQ5OysBC75bTHykPBAd4NuAopRoI4efMkoJm9xTjXhOuo10iwoa5d/OP3CUqonOsM4ksKXM2ghp4sUplNmsvfmlXAuk8pZC2V4/SWMRz1e9dTV/FxmV3fZJl22cIeY5KW2PcZZM4hrmluVa8JRIMxkAMwFE8iZTxZ+PFL4wi4yggA9zWxVkpSwVbFuSWC3LXpGJW1DaWyIzk0oxz5FEeYMBA+qj2il9spWhB7oDNyn7cFFFGhv2pD6WYbFstKvYCZIryLH5aDAlB4SGuUnxov+5l9mrPNSwFyUAjKZvSfdZO1pgZE5QW0cIAgnzzFE2pzWsSjQORfhgTA/NLvQj1OXh64GLcUtQW4fcs8gIk2rWJbPef5D/FQ7JR4Dq60tavyAFZ5cA8rKbAnbvSB1JX0ZC7Qev3CdgL+9szraiLjZU3j2Emn14rg/TsPnvvIFefPdfbWC/oYrltC6zoWIYTCb9qjVBjreApKZ6oKPegnNEEAHd/7qMTf8YM+JaF2phSWHdGfiNWc9EAxRtzO++xiLsMxncAH2SWFjG2QaSf38CnKPQBThvX/UvtTHTuZaN5G+1L9rUqszrRuPSLrrRwrufNh01BzDXrGpsOBrKeHQ6z65NV87ewyfzqIxqii1nt4QAhi3ktWxNC1e1TFib+R2g5Gu9JH07yad34qHbVcDfHx9el2QL3bt2LYf6EajMTiGwdmczaw0gOmG3TzU0TrkGR9VqDtVCf/yKjxu3/K5lFxXzVJWk+NO58GvWP+8grurKXrzSoVbMZylm8ITfi3OHoJQOtmmjv+zj0lr1k1csnR1e4JqnqftRswbmwUS9oDs1J/TQfXnrigQq1IW6ioztPcnpqMa0s9VO8XC57m/L8vyYCCrXUw2Esp7J4Go/STgNtKNqvIfGMM6nArgzuqB7BceJNO+qdQ2CZMH+I9l9u/Dia8T
x-amz-date
20260916T064547Z
x-amz-target
Firehose_20150804.PutRecordBatch
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Content-Type
application/x-amz-json-1.1

Response headers

Access-Control-Expose-Headers
x-amz-request-id,x-amz-id-2,x-amzn-RequestId,x-amzn-ErrorType,x-amzn-ErrorMessage,Date
Content-Encoding
gzip
x-amzn-RequestId
c292169b-3dc0-1201-a1b6-2bc044f31d66
Access-Control-Allow-Origin
*
Content-Length
279
Date
Wed, 16 Sep 2026 06:45:47 GMT
Content-Type
application/x-amz-json-1.1
x-amz-id-2
1xuulUebWbnmx/uHG+fHUIEkyJ8yRhj8AQi/h9FtwvhzrfzRjB5DaGBMZVMy8FT2N7sx8SPn399315ZGT/Ek8W5AkRa4dlEV
OPTIONS
H/1.1
200
OK
/
firehose.eu-west-1.amazonaws.com/ Frame
0
0
301ms
137ms
Preflight
99.80.34.227
Amazon.com
General
Full URL
https://firehose.eu-west-1.amazonaws.com/
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_128_GCM
Server
99.80.34.227 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-99-80-34-227.eu-west-1.compute.amazonaws.com
Software
/
Resource Hash

Request headers

Accept
*/*
Access-Control-Request-Headers
authorization,content-type,x-amz-date,x-amz-security-token,x-amz-target
Access-Control-Request-Method
POST
Origin
https://sklep.doppelherz.pl
Sec-Fetch-Mode
cors
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36

Response headers

Access-Control-Allow-Headers
authorization,content-type,x-amz-date,x-amz-security-token,x-amz-target
Access-Control-Allow-Methods
POST
Access-Control-Allow-Origin
*
Access-Control-Expose-Headers
x-amz-request-id,x-amz-id-2,x-amzn-RequestId,x-amzn-ErrorType,x-amzn-ErrorMessage,Date
Access-Control-Max-Age
172800
Content-Encoding
gzip
Content-Length
20
Date
Wed, 16 Sep 2026 06:45:47 GMT
x-amzn-RequestId
cd450842-abce-40ef-ae61-3519d2fd4f88
GET
H2
200
favicon.png
sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/
674 B
945 B
32ms
32ms
Other
image/png
77.79.221.168
ATMAN-ISP-AS Atma...
General
Full URL
https://sklep.doppelherz.pl/skins/user/rwd_shoper_42/images/favicon.png
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
77.79.221.168 Wieliszew, Poland, ASN15694 (ATMAN-ISP-AS Atman Sp. z o.o., PL),
Reverse DNS
ip-168.net-77-79-221-0.eco.atman.pl
Software
DCSaaS/httpd / DCSaaS
Resource Hash
4862a07078b7462e5d85a0a2ab5b49bc3667036e10fe2fbc04c4da9b7b3f8cfb
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=31536000
etag
"6aa0f517-2a2"
x-content-type-options
nosniff
expires
Thu, 16 Sep 2027 06:45:47 GMT
accept-ranges
bytes
content-length
674
date
Wed, 16 Sep 2026 06:45:47 GMT
x-xss-protection
1; mode=block
content-type
image/png
last-modified
Wed, 09 Sep 2026 05:56:39 GMT
x-powered-by
DCSaaS
server
DCSaaS/httpd
POST
H3
200
log_event Show response
www.youtube.com/youtubei/v1/ Frame 90C8
28 B
51 B
56ms
52ms
XHR
application/json
142.251.157.119
Google LLC
General
Full URL
https://www.youtube.com/youtubei/v1/log_event?alt=json
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.vgtVVePqX9U.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywF7JRG55jS5G2Q8ZG-NwvA9KK_XTA/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.157.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
scaffolding on HTTPServer2 /
Resource Hash
d7d5e54ad1e33d7ab49c664323ced79cb9723ff15e9764cd0edc3e15208e8336
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
X-YouTube-Client-Name
56
X-YouTube-Ad-Signals
dt=1789541145320&flash=0&frm=2&u_tz=120&u_his=1&u_h=1200&u_w=1600&u_ah=1200&u_aw=1600&u_cd=24&bc=31&bih=-12245933&biw=-12245933&brdim=80%2C80%2C80%2C80%2C1600%2C0%2C1600%2C1200%2C660%2C370&vis=1&wgl=true&ca_type=image
X-Goog-Event-Time
1789541148305
X-YouTube-Client-Version
2.20260915.01.00
Content-Type
application/json
X-YouTube-Page-Label
youtube.embeds.web_20260915_01_RC00
X-YouTube-Page-CL
981624205
X-YouTube-Utc-Offset
120
Referer
https://www.youtube.com/embed/RIenpVjeLR8?si=BHrZAFVtmPsydAwu
X-YouTube-Device
cbr=Chrome&cbrver=153.0.0.0&ceng=WebKit&cengver=537.36&cos=X11&cplatform=DESKTOP
X-Goog-Visitor-Id
CgswOEVkWl9sVlNaMCiY9qjVBjIoCgJQTBIiEh4SHAsMDg8QERITFBUWFxgZGhscHR4fICEiIyQlJicgH2LfAgrcAjIxLllUPVlDS0hsTVd3Ni14MUo0WkVoMFdnamZ2cUx4MHJUcm9lb2VEYWVUdjFuLXoxRDMxbzF3WVR0RnFlZHRKZUdqU3IxdDk3MkljZTVJdjRWc2F0Z2JPZnA0QUJvTGE3dmFoMHp1MEg0Q18xZXR6WnFObE9rd0l6QUN3UnpwcHF3YlhyOHgyWGFrVUUyVHk5bGZYZ0xiTXhPbDJLeWZUeXY5enhjdXNQaHBOMXpkS3pnbUlNaEtXcklVN0pVNkhzeS1ZS0EwZXZlclV2dWFPTkxROE9FM2dRSEVZRzU5SUI1bFRmd3dxUjB0Mk1zUllRRWFrRzBocEljZzQ4bWhjNXRSU2lzclhwNUx1SjY4eE04eXJzYmNHZFRRSm1Ma2RXVGFubG1wSFloQU1Vd3diQlRyX3VIQmlBLUdvRDBCLUtISG1lXzJ4bl8xLTQ1LVZYcEt5TE8xVjFCdw%3D%3D
X-Goog-Request-Time
1789541148305
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
X-YouTube-Time-Zone
Europe/Warsaw

Response headers

content-encoding
br
x-content-type-options
nosniff
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
31
date
Wed, 16 Sep 2026 06:45:48 GMT
x-xss-protection
0
content-type
application/json; charset=UTF-8
vary
Origin, X-Origin, Referer
server
scaffolding on HTTPServer2
x-frame-options
SAMEORIGIN
POST
H/1.1
200
OK
/ Show response
firehose.eu-west-1.amazonaws.com/
299 B
740 B
116ms
114ms
XHR
application/x-amz-json-1.1
99.80.34.227
Amazon.com
General
Full URL
https://firehose.eu-west-1.amazonaws.com/
Requested by
Host: js.smct.io
URL: https://js.smct.io/v7.14.0-beta.20/tag-v7.14.0-beta.20.js
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_128_GCM
Server
99.80.34.227 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-99-80-34-227.eu-west-1.compute.amazonaws.com
Software
/
Resource Hash
f853b689da6f6a36846e73f5c036f7c8e322404e4876746608b5d9766a5ff58e

Request headers

sec-ch-ua-platform
"Linux"
Authorization
AWS4-HMAC-SHA256 Credential=ASIAX2DUJRE4YGKK3LAD/20260916/eu-west-1/firehose/aws4_request, SignedHeaders=host;x-amz-date;x-amz-security-token;x-amz-target, Signature=8b30b2224c2a876a15e247780c84b459f0a3fee3938832b1840531d7b5ad108d
Referer
https://sklep.doppelherz.pl/
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
x-amz-security-token
IQoJb3JpZ2luX2VjEEcaCWV1LXdlc3QtMSJGMEQCIB113puMDL8jjvK++1+sh41UHbpa0v5tWZeZ5Wb9qp8QAiAjZd+DAtf5Hec3z8v6LYcgqJhsmvJUAt3NFva90wrO1yqvBQgQEAQaDDUzNzExNDgwNjU4NSIM1m5rXuifLzGzHrO2KowFfzko/pax4GipGsLl9Hg3tzxfFYNzvmlebGsVXA8jTWFCw4D+wZ9MNeAqaE8jTsqMSsXRuERoXbnYJovHaS1yjrXz5rgVZqDuxUOMPSZpMIEm09Gbio+7FZp2tOBdR2fOOtG2veM/lqBDh/zsG/Qgr769WneOIXTbeiCYfc+wOeKGVxMJI7JC/oBsYQhMS7GTlrSbwGXUjLJ75xkEDAhuGF7Hv56YBXZCYM08l2vMItKXW0mCjpwjgAVC6qBqGJ6P8RHlC8vHRSWH+Py5igxCeVS+1Qqa+VvoizQrruxTovvqZJdjwRvuoMTex1Eak4YoP4h24V+7bybttfJVNTegDo3h1oNk5xnSIO/yhzGGYbjUDTb6PqLHa/Jypi7jBWa2KiA7k0X9l26EI+hrZTlQ5OysBC75bTHykPBAd4NuAopRoI4efMkoJm9xTjXhOuo10iwoa5d/OP3CUqonOsM4ksKXM2ghp4sUplNmsvfmlXAuk8pZC2V4/SWMRz1e9dTV/FxmV3fZJl22cIeY5KW2PcZZM4hrmluVa8JRIMxkAMwFE8iZTxZ+PFL4wi4yggA9zWxVkpSwVbFuSWC3LXpGJW1DaWyIzk0oxz5FEeYMBA+qj2il9spWhB7oDNyn7cFFFGhv2pD6WYbFstKvYCZIryLH5aDAlB4SGuUnxov+5l9mrPNSwFyUAjKZvSfdZO1pgZE5QW0cIAgnzzFE2pzWsSjQORfhgTA/NLvQj1OXh64GLcUtQW4fcs8gIk2rWJbPef5D/FQ7JR4Dq60tavyAFZ5cA8rKbAnbvSB1JX0ZC7Qev3CdgL+9szraiLjZU3j2Emn14rg/TsPnvvIFefPdfbWC/oYrltC6zoWIYTCb9qjVBjreApKZ6oKPegnNEEAHd/7qMTf8YM+JaF2phSWHdGfiNWc9EAxRtzO++xiLsMxncAH2SWFjG2QaSf38CnKPQBThvX/UvtTHTuZaN5G+1L9rUqszrRuPSLrrRwrufNh01BzDXrGpsOBrKeHQ6z65NV87ewyfzqIxqii1nt4QAhi3ktWxNC1e1TFib+R2g5Gu9JH07yad34qHbVcDfHx9el2QL3bt2LYf6EajMTiGwdmczaw0gOmG3TzU0TrkGR9VqDtVCf/yKjxu3/K5lFxXzVJWk+NO58GvWP+8grurKXrzSoVbMZylm8ITfi3OHoJQOtmmjv+zj0lr1k1csnR1e4JqnqftRswbmwUS9oDs1J/TQfXnrigQq1IW6ioztPcnpqMa0s9VO8XC57m/L8vyYCCrXUw2Esp7J4Go/STgNtKNqvIfGMM6nArgzuqB7BceJNO+qdQ2CZMH+I9l9u/Dia8T
x-amz-date
20260916T064547Z
x-amz-target
Firehose_20150804.PutRecordBatch
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Content-Type
application/x-amz-json-1.1

Response headers

Access-Control-Expose-Headers
x-amz-request-id,x-amz-id-2,x-amzn-RequestId,x-amzn-ErrorType,x-amzn-ErrorMessage,Date
Content-Encoding
gzip
x-amzn-RequestId
d2b07620-42e6-9dfe-b194-4b7c3bd59299
Access-Control-Allow-Origin
*
Content-Length
280
Date
Wed, 16 Sep 2026 06:45:48 GMT
Content-Type
application/x-amz-json-1.1
x-amz-id-2
WkTOxImXG3ix8sgcoL2Oa/ZB+naeIKCQjPMkcHTbYSExHbeqkgsJqgJDQXnE2dF/Ip5eaA71783A18+J5MapvmeUEtSxf9T3
POST
H3
202
analytics
inpostpay-widget-api.inpost.pl/v1/inpostpay/widget/
0
0
142ms
110ms
Fetch
104.18.41.61
Cloudflare
General
Full URL
https://inpostpay-widget-api.inpost.pl/v1/inpostpay/widget/analytics
Requested by
Host: inpostpay-widget-v2.inpost.pl
URL: https://inpostpay-widget-v2.inpost.pl/inpostpay.widget.v2.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.18.41.61 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
Security Headers
Name Value
Strict-Transport-Security max-age=31536000 ; includeSubDomains
X-Content-Type-Options nosniff
X-Frame-Options DENY

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

x-correlation-id
89ee1dda-3e40-4274-abdb-9ee98b329cdc
cf-cache-status
DYNAMIC
access-control-allow-methods
GET,PUT,POST
x-content-type-options
nosniff
expires
0
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Wed, 16 Sep 2026 06:45:48 GMT
priority
u=1,i
x-frame-options
DENY
strict-transport-security
max-age=31536000 ; includeSubDomains
cache-control
no-cache, no-store, max-age=0, must-revalidate
pragma
no-cache
referrer-policy
no-referrer
via
1.1 google
cf-ray
a3bde911ad328732-WAW
access-control-allow-origin
*
content-length
0
server
cloudflare
GET
H3
200
ca.js Show response
rd.afftrack.pro/
506 B
862 B
80ms
35ms
Script
application/javascript
188.114.96.3
Cloudflare
General
Full URL
https://rd.afftrack.pro/ca.js
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
188.114.96.3 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare / Express
Resource Hash
eb47a6bcd058832111e35209b3dbd1900afc44ac854f7588f2d9927e1757a54d

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
zstd
cf-cache-status
HIT
etag
W/"1fa-WYeRn42UHXNU32rl43hziW6zO/o"
age
0
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=RCnbR3Jyzwfra%2B6srks%2Fa5vQZz95VCont1cEhdHl8xof75n4eudTtQz3YATrPDE9%2Bft3LWfbRzAYrlFbkwDpj65TWBsIcNeRc7byXSD%2BVjz7Ghvc0QZdJao6oGEjz6XXEvg%3D"}]}
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Wed, 16 Sep 2026 06:45:49 GMT
content-type
application/javascript; charset=utf-8
vary
Origin
priority
u=3,i=?0
cache-control
public, max-age=14400
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
access-control-allow-credentials
true
cf-ray
a3bde9156d0a714a-WAW
x-powered-by
Express
server
cloudflare
GET

ZQK-JIAO2K.js
tags.fulllab.com.br/scripts/
0
0


GET
H3
200
Y4M4yB.js Show response
s.retargeted.co/1/
688 B
998 B
106ms
63ms
Script
text/plain
188.114.97.3
Cloudflare
General
Full URL
https://s.retargeted.co/1/Y4M4yB.js
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
188.114.97.3 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
3d15410482ba2dce1cd463f73e97396affe54bfde9f3a61dc89a8af1c993eac4

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

surrogate-control
no-store
content-encoding
zstd
cf-cache-status
BYPASS
etag
W/"2b0-k8BN+7vHJ5MwGB9UY9Hw7vUhr6c"
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=AY23DZ7gXSUBvZeRP%2FI6uOJieXqSeKH2dBGA8J7Aq88mzTRhVB90Ih7Ulp9GcrSetjcnlHsBnJ8aLbR6RUVWoliY84uyQ5vyku4OTDAxV3OhIwHf%2FyqsCZ3Vv0TtHuAwcbw%3D"}]}
expires
0
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Wed, 16 Sep 2026 06:45:49 GMT
content-type
text/plain; charset=utf-8
content-disposition
inline
priority
u=3,i=?0
cache-control
no-store, no-cache, must-revalidate, proxy-revalidate
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
cf-ray
a3bde9155afe9a50-WAW
access-control-allow-origin
*
server
cloudflare
GET
H2
200
r.php Show response
apptracker.stream/
Redirect Chain
  • https://bbd-tag.de/r/75395-product.js?gdpr=0&gdpr_consent=
  • https://apptracker.stream/r.php?t=75395&p=product&gdpr=0&gdpr_consent=
0
620 B
371ms
157ms
Script
application/javascript
82.223.103.149
IONOS-AS IONOS SE
General
Full URL
https://apptracker.stream/r.php?t=75395&p=product&gdpr=0&gdpr_consent=
Protocol
H2
Server
82.223.103.149 , Spain, ASN8560 (IONOS-AS IONOS SE, DE),
Reverse DNS
Software
nginx/1.14.0 (Ubuntu) /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Referer
https://sklep.doppelherz.pl/

Response headers

cache-control
no-store, no-cache, must-revalidate, max-age=0, post-check=0, pre-check=0
pragma
no-cache
expires
on, 01 Jan 1970 00:00:00 GMT
p3p
CP="CURa ADMa DEVa PSAo PSDo OUR BUS UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
date
Wed, 16 Sep 2026 06:45:49 GMT
content-type
application/javascript
last-modified
Wed, 16 Sep 2026 06:45:49 GMT
server
nginx/1.14.0 (Ubuntu)

Redirect headers

location
https://apptracker.stream/r.php?t=75395&p=product&gdpr=0&gdpr_consent=
content-length
170
date
Wed, 16 Sep 2026 06:45:49 GMT
content-type
text/html
server
nginx/1.14.0 (Ubuntu)
GET
H/1.1
200
OK
product.d Show response
js.cookieless-data.com/
3 KB
2 KB
315ms
131ms
Script
text/javascript
212.129.3.113
AS12876 Scaleway SAS
General
Full URL
https://js.cookieless-data.com/product.d?pa=33208&r=&u=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&cat_id=Doppelherz%20system&product_id=412
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_256_GCM
Server
212.129.3.113 Paris, France, ASN12876 (AS12876 Scaleway SAS, FR),
Reverse DNS
online-prod.ipsfailover.com
Software
nginx/1.20.2 /
Resource Hash
1b366d882f8320890ed6d040705b9dcff4cbfa1b0422d9c1972e54bccaa395c8
Security Headers
Name Value
Strict-Transport-Security max-age=15724800; includeSubDomains; preload
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

Transfer-Encoding
chunked
Strict-Transport-Security
max-age=15724800; includeSubDomains; preload
Cache-Control
no-store, no-cache, must-revalidate, max-age=0, post-check=0, pre-check=0
Content-Encoding
gzip
Pragma
no-cache
Connection
keep-alive
Cross-Origin-Resource-Policy
cross-origin
Expires
Tue, 01 Jan 2000 00:00:00 GMT
Access-Control-Allow-Origin
*
P3p
CP="NOI DSP COR ADM PSAo PSDo OURo SAMo UNRo OTRo BUS COM NAV DEM STA PRE"
Date
Wed, 16 Sep 2026 06:45:49 GMT
X-Xss-Protection
0
Content-Type
text/javascript
Server
nginx/1.20.2
GET
H/1.1
200
OK
lod Show response
altopd.com/
1 KB
918 B
303ms
120ms
Script
text/javascript
18.197.44.30
Amazon.com
General
Full URL
https://altopd.com/lod
Requested by
Host: dfd.doppelherz.pl
URL: https://dfd.doppelherz.pl/u/37/p75395.js
Protocol
HTTP/1.1
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
18.197.44.30 Frankfurt am Main, Germany, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-18-197-44-30.eu-central-1.compute.amazonaws.com
Software
nginx /
Resource Hash
5351e5f1d2ee39e720c2b16dc59b3d241373085a281f891cd93da9596789418b

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

Transfer-Encoding
chunked
Cache-Control
no-store, no-cache, private
Content-Encoding
gzip
Pragma
no-cache
Connection
keep-alive
Date
Wed, 16 Sep 2026 06:45:49 GMT
Content-Type
text/javascript
Server
nginx
GET
H2
200
ptag.js Show response
cdn.preciso.net/aud/clientjs/
4 KB
2 KB
135ms
35ms
Script
text/javascript
104.18.0.2
Cloudflare
General
Full URL
https://cdn.preciso.net/aud/clientjs/ptag.js?3987
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.18.0.2 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
de7206e6b64cbebf681f979f3b134a27a5e0c00f2c3bd1f1f4ad4e500ee97685

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
access-control-expose-headers
Content-Length,Content-Range,Accept-Ranges
x-goog-hash
crc32c=pGdhMw==, md5=7sCcFrUQoRHhdHuXfpQAag==
content-encoding
br
etag
W/"eec09c16b510a111e1747b977e94006a"
age
1060
cf-cache-status
HIT
access-control-allow-methods
GET,HEAD,OPTIONS
x-goog-stored-content-encoding
identity
x-goog-stored-content-length
3922
date
Wed, 16 Sep 2026 06:45:49 GMT
content-type
text/javascript
last-modified
Mon, 18 May 2026 05:29:28 GMT
vary
Accept-Encoding
x-guploader-uploadid
AJjja9Y--r1e1Cas6WiOqFrLOILI-KmdEHL4tPgghqOD0f6RRIlwgsg20kfelzquLvl14Tb6wWgmQUo
access-control-allow-headers
Origin,Range,Accept,Content-Type,Authorization,X-Requested-With
cache-control
public,max-age=86400
x-goog-storage-class
STANDARD
via
1.1 google
cf-ray
a3bde915bb8d0716-WAW
x-amz-checksum-crc32c
pGdhMw==
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1779082168785375
content-length
1053
server
cloudflare
GET

asyncjs.php
rev.owltrack.com/d/
0
0


GET
H3
200
ptag.js Show response
cdn.logico3c.com/aud/clientjs/
4 KB
2 KB
80ms
38ms
Script
text/javascript
172.67.150.171
Cloudflare
General
Full URL
https://cdn.logico3c.com/aud/clientjs/ptag.js?8879
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.67.150.171 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
d5c591af27dba359f1fb822e5d0b1e23750fff8a86ea55e7b30c950fbd35a6ca

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
access-control-expose-headers
Content-Length,Content-Range,Accept-Ranges
x-goog-hash
crc32c=MCVwKQ==, md5=+s+1rnBFz67YOZ7VJfzIDQ==
content-encoding
br
etag
W/"facfb5ae7045cfaed8399ed525fcc80d"
cf-cache-status
REVALIDATED
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=6Ztf3YUR6Y2SnpBQ9ZPBdhgUKZ7oud6%2BfHf%2BAiqiGQlVPdkElX9CtrnLNfkdtWEi2dIlklDQbNNYWAEHNCQSwTBwYceT1xMtPt%2FRG6hT5Bw4kMS2puv11OGBjxiiHI27pZiR"}]}
access-control-allow-methods
GET,HEAD,OPTIONS
x-goog-stored-content-encoding
identity
alt-svc
h3=":443"; ma=86400
x-goog-stored-content-length
3821
server-timing
cfExtPri
date
Wed, 16 Sep 2026 06:45:49 GMT
content-type
text/javascript
vary
Accept-Encoding
last-modified
Thu, 30 Apr 2026 11:16:46 GMT
x-guploader-uploadid
AJjja9YF0RbdYuWJi6cWLv64TrT5L860MGNB2ub52oTVLV3t5VmaK9A2oSz6uU5elcy7HHrCFRiUhGY
access-control-allow-headers
Origin,Range,Accept,Content-Type,Authorization,X-Requested-With
priority
u=3,i=?0
cache-control
public,max-age=1800
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
cdn-cache-control
max-age=0, must-revalidate
x-goog-storage-class
STANDARD
via
1.1 google
cf-ray
a3bde915599a028c-WAW
x-amz-checksum-crc32c
MCVwKQ==
accept-ranges
none
access-control-allow-origin
*
x-goog-generation
1777547806014429
server
cloudflare
GET
H2
200
67dc16df875f8d5290258ea2.js Show response
trk.retagtraffic.com/rtg/
830 B
1 KB
159ms
43ms
Script
text/javascript
188.114.96.3
Cloudflare
General
Full URL
https://trk.retagtraffic.com/rtg/67dc16df875f8d5290258ea2.js
Requested by
Host: dfd.doppelherz.pl
URL: https://dfd.doppelherz.pl/u/37/p75395.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
188.114.96.3 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
bdccf500c0b0c6bbee6a615f19941c79181ab729da53fdd598bc8aee485015d4

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
x-goog-hash
crc32c=awPzZg==, md5=Wf7w8l0EZfIsDqEfcydIeA==
cf-cache-status
HIT
etag
W/"59fef0f25d0465f22c0ea11f73274878"
age
522
content-encoding
zstd
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=VPbGot1exBr6Y5JOHpBsyqNfmGMIUcMMBZVcMsMCLkSKk95ua%2FBfAM6zhYde9m%2F8U%2BNjYQBUzcwlfvEqS3C8nBKRx8zkWxJcMMPVqc49ZdKrMJmybU41J4WgsbQIVOrZRVVuOIW1Mg%3D%3D"}]}
x-goog-stored-content-encoding
identity
alt-svc
h3=":443"; ma=86400
x-goog-stored-content-length
830
date
Wed, 16 Sep 2026 06:45:49 GMT
content-type
text/javascript
last-modified
Thu, 03 Apr 2025 14:37:35 GMT
x-guploader-uploadid
AKhXX7J1lFLIZwQkX65Sq29e6YpB5mfIDHA0L1z_hPHRYHiOEqkHSJAz7InHzEfP6U9EERbp-nnot3I
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
cache-control
public, max-age=14400
x-goog-storage-class
STANDARD
cf-ray
a3bde915dce05f09-WAW
x-goog-generation
1743691055440356
server
cloudflare
GET
H3
200
collect.js Show response
tag.facemyads.co/xdP1Vx/
86 KB
32 KB
120ms
73ms
Script
text/plain
188.114.96.3
Cloudflare
General
Full URL
https://tag.facemyads.co/xdP1Vx/collect.js
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
188.114.96.3 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
538fb816c4684719da4b865541678b8989a21b87509951b3e0605a943e5b28db

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

surrogate-control
no-store
content-encoding
zstd
cf-cache-status
BYPASS
etag
W/"1573b-abM0VoLXRNf7h3laybzDzLgtH60"
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=UlhE2Rn4pPQKL9Hc78wFhX6pAujqPuWFG55LUasry0oHZUgvYBIUhITPtUJUt61DEH%2BtdhKfHmZiKWzQQiAC%2Bse8tGoIAqnFoHtjGTKp%2FQft0S7ADNci04WzzgGDN1kXbv0P"}]}
expires
0
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Wed, 16 Sep 2026 06:45:49 GMT
content-type
text/plain; charset=utf-8
content-disposition
inline
priority
u=3,i=?0
cache-control
no-store, no-cache, must-revalidate, proxy-revalidate
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
cf-ray
a3bde9158aac651d-WAW
access-control-allow-origin
*
server
cloudflare
GET
H2
200
retar.php Show response
vu.adschoom.com/trafic/
8 KB
9 KB
276ms
114ms
Script
text/javascript
51.210.24.88
OVH OVH SAS
General
Full URL
https://vu.adschoom.com/trafic/retar.php?boutique=Doppelherzpl&type=PRODUIT&produit_id=412&gdpr_consent=&topfr=https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus&topfr2=
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
51.210.24.88 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
ns3257326.ip-51-210-24.eu
Software
nginx/1.24.0 (Ubuntu) /
Resource Hash
c9c3d8b7bddb02e9da5196a4568ee666123b9db82764e6e76bd74781a456949b

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

expires
Sun, 06 Sep 2026 06:45:49 GMT
cache-control
no-store, no-cache, must-revalidate, post-check=0, pre-check=0
date
Wed, 16 Sep 2026 06:45:49 GMT
pragma
no-cache
content-type
text/javascript;charset=UTF-8
server
nginx/1.24.0 (Ubuntu)
GET
H/1.1
200
OK
data.php Show response
pixel.bsmartdata.com/
0
369 B
281ms
137ms
Script
text/html
78.46.234.191
HETZNER-AS Hetzne...
General
Full URL
https://pixel.bsmartdata.com/data.php?type=js&cid=net_net_75395&loc=product&val=412&gdpr=0&gdpr_consent=
Requested by
Host: dfd.doppelherz.pl
URL: https://dfd.doppelherz.pl/u/37/p75395.js
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_128_GCM
Server
78.46.234.191 Falkenstein, Germany, ASN24940 (HETZNER-AS Hetzner Online GmbH, DE),
Reverse DNS
static.191.234.46.78.clients.your-server.de
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

Transfer-Encoding
chunked
Cache-Control
no-cache, private
Content-Encoding
gzip
Connection
keep-alive
Access-Control-Allow-Methods
POST, GET
Access-Control-Allow-Origin
*
Date
Wed, 16 Sep 2026 06:45:49 GMT
Content-Type
text/html; charset=utf-8
Server
nginx
Access-Control-Allow-Headers
Content-Type
GET
H2
200
code.js Show response
rtg.wewomedia.com/track/
2 KB
1 KB
178ms
53ms
Script
application/javascript
34.102.157.203
Google LLC
General
Full URL
https://rtg.wewomedia.com/track/code.js
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.102.157.203 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
203.157.102.34.bc.googleusercontent.com
Software
/
Resource Hash
6c357c6789e3c945e2e6e88ae3eb1b641c90bb8ab45c1c1b18c112aff6cbcf04

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

via
1.1 google
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-encoding
zstd
content-length
1025
date
Wed, 16 Sep 2026 06:45:49 GMT
content-type
application/javascript;charset=UTF-8
vary
Accept-Encoding
GET
H3
200
js Show response
mediaconvertly.com/src/resource/
3 KB
2 KB
210ms
153ms
Script
text/javascript
104.21.10.19
Cloudflare
General
Full URL
https://mediaconvertly.com/src/resource/js?tag=ZQK-JIAO2K
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.21.10.19 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
57a0d0328187c357c348e41654bd8afd77fda3dfccf9563dcfef61a297babf4e

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-store, no-cache, must-revalidate, post-check=0, pre-check=0
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
content-encoding
zstd
cf-cache-status
DYNAMIC
pragma
no-cache
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=4X9bYgtZTX3NENeHVNDlaxzUxE30r8rByANJpOApYFU%2F3odoWtSNUC2CBrT7wyhwSjfn9fZmyxlmaZsDp3Ltk8hEXcbqI8q8O0KgkhBeZvVb48Mn3azKzAqL%2FlvoX42smZHtINE%3D"}]}
cf-ray
a3bde9165ae7bfe9-WAW
expires
0
access-control-allow-origin
*
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Wed, 16 Sep 2026 06:45:49 GMT
content-type
text/javascript
server
cloudflare
priority
u=3,i=?0
GET
H2
200
6a743395c3538afa3704b77a.js Show response
static-cdn.trackier.com/rtg/
1 KB
953 B
126ms
31ms
Script
text/javascript
34.149.104.117
Google LLC
General
Full URL
https://static-cdn.trackier.com/rtg/6a743395c3538afa3704b77a.js
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.149.104.117 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
117.104.149.34.bc.googleusercontent.com
Software
UploadServer /
Resource Hash
fcd1e5bf7576c1520e9805247e923cd6efd2d346376b20f94dd07f445b82fc4c

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
x-goog-hash
crc32c=AN3Gmw==, md5=6msTLrNsFjLQmVpMSlX/rA==
content-encoding
br
etag
W/"ea6b132eb36c1632d0995a4c4a55ffac"
age
2783
x-goog-stored-content-encoding
identity
alt-svc
h3=":443"; ma=2592000
x-goog-stored-content-length
1088
date
Wed, 16 Sep 2026 05:59:26 GMT
last-modified
Tue, 01 Sep 2026 12:46:41 GMT
vary
Accept-Encoding
content-type
text/javascript
x-guploader-uploadid
AJjja9YFkLbSGlfuiGnjcjDLiFXYTsnKST1zCPElgC1fMFFV0XU5Q4CTueiTo2KYHZ2DOHIv
cache-control
public,max-age=3600
x-goog-storage-class
STANDARD
accept-ranges
none
x-goog-generation
1788266801608014
content-length
505
server
UploadServer
GET
H2
200
rzbws5
mrtg.emailpartners.net/a/v/
43 B
597 B
278ms
126ms
Image
image/gif
51.38.158.176
OVH OVH SAS
General
Full URL
https://mrtg.emailpartners.net/a/v/rzbws5?referer=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&pid=412
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
51.38.158.176 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
ip176.ip-51-38-158.eu
Software
nginx / React/alpha
Resource Hash
aa03dc59bdca72631d2301e4297cfa030bd31b907dc138e7b973d12311c90a22

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
private, must-revalidate
pragma
no-cache
expires
-1
content-length
43
date
Wed, 16 Sep 2026 06:45:49 GMT
content-type
image/gif
x-powered-by
React/alpha
server
nginx
GET
H2
200
p
d.audiencerun.com/t/okn/
43 B
845 B
649ms
327ms
Image
image/gif
3.131.73.36
Amazon.com
General
Full URL
https://d.audiencerun.com/t/okn/p?idn=75395&gdpr=0&gdpr_consent=&r=&p=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&cachebuster=LLqRb4Z54OFsbUY
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
3.131.73.36 Columbus, United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-3-131-73-36.us-east-2.compute.amazonaws.com
Software
nginx /
Resource Hash
548f2d6f4d0d820c6c5ffbeffcbd7f0e73193e2932eefe542accc84762deec87

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

date
Wed, 16 Sep 2026 06:45:49 GMT
content-type
image/gif
server
nginx
GET
H2
204
/ Show response
ai.trk42.net/
0
138 B
175ms
75ms
Script
application/javascript
216.239.36.21
Google LLC
General
Full URL
https://ai.trk42.net/?cid={TOKEN}
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
216.239.36.21 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
any-in-2415.1e100.net
Software
Google Frontend / Express
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

date
Wed, 16 Sep 2026 06:45:49 GMT
content-type
application/javascript; charset=utf-8
x-powered-by
Express
server
Google Frontend
x-cloud-trace-context
aed3fe51f9c4b9205bfaf97827b3f5ff
GET
H2
200
/ Show response
p.gsitrix.com/page/ Frame D8C3
42 KB
42 KB
198ms
63ms
Script
application/javascript
85.195.93.95
VELIANET-AS velia...
General
Full URL
https://p.gsitrix.com/page/?a=60ef70b6a8b131626304694&p=product&prid={IDPRODUIT}&av=0&as=trafficpark&ax=1&w=doppelherz.pl&gdpr={GDPR}&gdpr_consent={GDPR_CONSENT}&ref={PAGE}
Requested by
Host:
URL: about:srcdoc
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
85.195.93.95 Frankfurt am Main, Germany, ASN29066 (VELIANET-AS velia.net Internetdienste GmbH, DE),
Reverse DNS
Software
/
Resource Hash
7e8d91e33c298ffdaf81c29a4deb12ee1a0ff1ea5947785ac385ed0b0337c17d

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
post-check=0, pre-check=0
pragma
no-cache
access-control-allow-credentials
true
access-control-allow-methods
*
expires
Sat, 13 Jun 1992 00:00:00 GMT
access-control-allow-origin
*
p3p
CP="NOI DEVa TAIa OUR BUS UNI"
date
Wed, 16 Sep 2026 06:45:49 GMT
content-type
application/javascript; charset=utf-8
access-control-allow-headers
*
GET
H3
200
beacon-apstje.js Show response
afftrack.pro/api/v1/script/c028ec8c-2f80-4c3b-b988-e72fbfa2b3e8/
6 KB
3 KB
44ms
34ms
Script
application/javascript
188.114.96.3
Cloudflare
General
Full URL
https://afftrack.pro/api/v1/script/c028ec8c-2f80-4c3b-b988-e72fbfa2b3e8/beacon-apstje.js?p=c028ec8c-2f80-4c3b-b988-e72fbfa2b3e8
Requested by
Host: rd.afftrack.pro
URL: https://rd.afftrack.pro/ca.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
188.114.96.3 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare / Express
Resource Hash
d0a7fe248eb05e77c77dfd4cdfb32e6ab9ce59458f1e8716fc1dec4c080963de

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
zstd
cf-cache-status
HIT
etag
W/"173f-w3kxsqBDhP7QFKyjXrowuouEYVo"
age
79
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=IYe1C61vud8KqBMQW86wy3qjzFSm%2Fdg119d5Nu7bBuJ96%2FZK30BJbR9Equb8cjXResqwuqEP55n6eB6ybZAthW0J8cjiHiYjQT6bFaWD97cb1nli9RNN3UzPPalLQcY%3D"}]}
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Wed, 16 Sep 2026 06:45:49 GMT
content-type
application/javascript; charset=utf-8
vary
Origin
priority
u=3,i=?0
cache-control
public, max-age=14400
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
access-control-allow-credentials
true
cf-ray
a3bde91718a9714a-WAW
x-powered-by
Express
server
cloudflare
GET
H3
200
8879.js Show response
cdn.logico3c.com/tag/obj/js/
6 KB
3 KB
36ms
35ms
Script
text/plain
172.67.150.171
Cloudflare
General
Full URL
https://cdn.logico3c.com/tag/obj/js/8879.js?
Requested by
Host: cdn.logico3c.com
URL: https://cdn.logico3c.com/aud/clientjs/ptag.js?8879
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.67.150.171 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
8acc1e9aed8df67ce763aae3c9d9ff6f6b963eacab2009c17c0395f88b5aea1e

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
access-control-expose-headers
Content-Length,Content-Range,Accept-Ranges
x-goog-hash
crc32c=zWl9gA==, md5=kiwq3KnzWlhmZS3nSysYTA==
content-encoding
br
etag
W/"922c2adca9f35a5866652de74b2b184c"
cf-cache-status
REVALIDATED
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=8LGDbuoKb5Jb0tj0nfZbO41IxVdmkTSm604yEFvqp5Nw4ArDQpj%2FI5TbfOveKAKCmnohUanINP31nyyYGnG0jjZwfNbyNUQaaSMNaT56XV0kRILeLgrJb0LRJxdT9Gp1z6Hh"}]}
access-control-allow-methods
GET,HEAD,OPTIONS
x-goog-stored-content-encoding
identity
alt-svc
h3=":443"; ma=86400
x-goog-stored-content-length
5915
server-timing
cfExtPri
date
Wed, 16 Sep 2026 06:45:49 GMT
content-type
text/plain
vary
Accept-Encoding
last-modified
Sat, 08 Aug 2026 07:58:00 GMT
x-guploader-uploadid
AJjja9bYISHifG8MHuRJzoIt6-daF1KyF0mw5QbOkcjCRypAESX08UENHK8dzFQ55b01k0tyqcmHk5M
access-control-allow-headers
Origin,Range,Accept,Content-Type,Authorization,X-Requested-With
priority
u=3,i=?0
cache-control
public,max-age=1800
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
cdn-cache-control
max-age=0, must-revalidate
x-goog-storage-class
STANDARD
via
1.1 google
cf-ray
a3bde915a9a0028c-WAW
x-amz-checksum-crc32c
zWl9gA==
accept-ranges
none
access-control-allow-origin
*
x-goog-generation
1786175880916173
server
cloudflare
GET
H3
200
Y4M4yB.js Show response
s.retargeted.co/2/
86 KB
32 KB
79ms
79ms
Script
text/plain
188.114.97.3
Cloudflare
General
Full URL
https://s.retargeted.co/2/Y4M4yB.js
Requested by
Host: s.retargeted.co
URL: https://s.retargeted.co/1/Y4M4yB.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
188.114.97.3 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
b5c0bc721b9625d08a45be005e83ef7143e3b8640afef96a3283f53d2f3bec82

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

surrogate-control
no-store
content-encoding
zstd
cf-cache-status
BYPASS
etag
W/"1573b-aoaijEG5WEoNTRyGXXopsDRRvTU"
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=6uw9oUtFgOgX3zfnD1mxa1VQ9SD4EUOMy8nO9WPpZDN%2FCO%2FX4JMpBGVZ5CbsphNmDZm7LHGxtNPL4Cw0u%2B7ewl3jBpUF1cReSuoyX2GOG%2FJqJspOmlA%2Ff2ZUNgBeELHBZ5g%3D"}]}
expires
0
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Wed, 16 Sep 2026 06:45:49 GMT
content-type
text/plain; charset=utf-8
content-disposition
inline
priority
u=3,i=?0
cache-control
no-store, no-cache, must-revalidate, proxy-revalidate
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
cf-ray
a3bde915cbbe9a50-WAW
access-control-allow-origin
*
server
cloudflare
GET
H2
200
3987.js Show response
cdn.preciso.net/aud/clientjs/
6 KB
2 KB
47ms
46ms
Script
text/plain
104.18.0.2
Cloudflare
General
Full URL
https://cdn.preciso.net/aud/clientjs/3987.js?
Requested by
Host: cdn.preciso.net
URL: https://cdn.preciso.net/aud/clientjs/ptag.js?3987
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.18.0.2 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
7b0e1348f28fb277b049d55cf086b1e7baf7cc06d9de37c6c7ae2941fc759acc

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
access-control-expose-headers
Content-Length,Content-Range,Accept-Ranges
x-goog-hash
crc32c=u10mjg==, md5=NHq+JN+pJh1M4yf8uziTyQ==
content-encoding
br
etag
W/"347abe24dfa9261d4ce327fcbb3893c9"
age
1060
cf-cache-status
HIT
access-control-allow-methods
GET,HEAD,OPTIONS
x-goog-stored-content-encoding
identity
x-goog-stored-content-length
5920
date
Wed, 16 Sep 2026 06:45:49 GMT
content-type
text/plain
last-modified
Thu, 13 Aug 2026 06:17:55 GMT
vary
Accept-Encoding
x-guploader-uploadid
AJjja9ZR7J8Ou7jWPw_PgIEKMOy0e1foa21n4O22kf4jrNFIjlASplZNYZlOZnB3uZhP5lCTrOl20mM
access-control-allow-headers
Origin,Range,Accept,Content-Type,Authorization,X-Requested-With
cache-control
public,max-age=86400
x-goog-storage-class
STANDARD
via
1.1 google
cf-ray
a3bde9162c6c0716-WAW
x-amz-checksum-crc32c
u10mjg==
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1786601875524035
content-length
2142
server
cloudflare
GET
H3
200
ret.js Show response
loopwidget.com/
4 KB
2 KB
80ms
35ms
Script
application/javascript
188.114.97.3
Cloudflare
General
Full URL
https://loopwidget.com/ret.js
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
188.114.97.3 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare / Express
Resource Hash
823b0d21e4f3045ae381c91e418036c91449acbd965333ef1dedeb96011dc021

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
zstd
cf-cache-status
HIT
etag
W/"108d-dKyj+veKYNM9YyUZJmER6sXx5C8"
age
1420
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=K78A2Sq3y3LSyb3AcNZwjR%2F9ubJuwmwbsW1UWigOwPeO19QwoU61H7cVk3zxwa5yHcD4zCIFX8sZW9poocIZm%2BfWcLHjxgAm0j52HY4jWoFF3xvLqiwCo87jXdvv0Lev2A%3D%3D"}]}
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Wed, 16 Sep 2026 06:45:49 GMT
content-type
application/javascript; charset=utf-8
priority
u=3,i=?0
cache-control
max-age=14400
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
cf-ray
a3bde9175c5e0935-WAW
access-control-allow-origin
*
x-powered-by
Express
server
cloudflare
GET
H2
200
cookiematch.aspx Show response
ban.tangooserver.com/rtb/google/ Frame 336D
Redirect Chain
  • https://cm.g.doubleclick.net/pixel?google_nid=tangoomedia&google_ula=7241462486&google_cm&cok15=kwo_dpp_pl&cnty15=POL&t=4&ProgramName=DOPPELHERZ_PL8879&AudienceId=8879&CampaignId=65997&Referrer=htt...
  • https://ban.tangooserver.com/rtb/google/cookiematch.aspx?id=tangoomedia&cok15=kwo_dpp_pl&cnty15=POL&t=4&ProgramName=DOPPELHERZ_PL8879&AudienceId=8879&CampaignId=65997&Referrer=https%3A%2F%2Fsklep.d...
109 B
189 B
60ms
60ms
Document
text/html
104.18.31.101
Cloudflare
General
Full URL
https://ban.tangooserver.com/rtb/google/cookiematch.aspx?id=tangoomedia&cok15=kwo_dpp_pl&cnty15=POL&t=4&ProgramName=DOPPELHERZ_PL8879&AudienceId=8879&CampaignId=65997&Referrer=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&ProductId=412&ProductCategoryList=Doppelherz%20system&PageType=product&Browsercheck=true&gdpr=0&a15=false&dw15=false&ls15=false&google_gid=CAESEEiSW-Fd8L3g4FnCSbvue8c&google_cver=1&google_ula=7241462486,0
Requested by
Host: cdn.logico3c.com
URL: https://cdn.logico3c.com/tag/obj/js/8879.js?
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.18.31.101 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
6d3583a3f5dbc4ce59ea437e238a52ce5e8c9c948f64176233d92b3a772eea3a
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://sklep.doppelherz.pl/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

cache-control
no-cache, no-store, max-age=0, must-revalidate
cf-cache-status
DYNAMIC
cf-ray
a3bde916ebbe3463-WAW
content-encoding
gzip
content-type
text/html;charset=ISO-8859-1
date
Wed, 16 Sep 2026 06:45:49 GMT
expires
0
pragma
no-cache
referrer-policy
unsafe-url
server
cloudflare
vary
Origin,Access-Control-Request-Method,Access-Control-Request-Headers
via
1.1 google
x-content-type-options
nosniff
x-xss-protection
0

Redirect headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cache-control
no-cache, must-revalidate
content-length
723
content-type
text/html; charset=UTF-8
cross-origin-resource-policy
cross-origin
date
Wed, 16 Sep 2026 06:45:49 GMT
expires
Fri, 01 Jan 1990 00:00:00 GMT
location
https://ban.tangooserver.com/rtb/google/cookiematch.aspx?id=tangoomedia&cok15=kwo_dpp_pl&cnty15=POL&t=4&ProgramName=DOPPELHERZ_PL8879&AudienceId=8879&CampaignId=65997&Referrer=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&ProductId=412&ProductCategoryList=Doppelherz%20system&PageType=product&Browsercheck=true&gdpr=0&a15=false&dw15=false&ls15=false&google_gid=CAESEEiSW-Fd8L3g4FnCSbvue8c&google_cver=1&google_ula=7241462486,0
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
pragma
no-cache
server
HTTP server (unknown)
x-xss-protection
0
GET

audit.aspx
ban.tangooserver.com/
0
0


GET
H/1.1
200
OK
sys.php Show response
o.gsitrix.com/ Frame D8C3
16 KB
16 KB
232ms
104ms
Script
application/x-javascript
85.195.73.74
VELIANET-AS velia...
General
Full URL
https://o.gsitrix.com/sys.php?a=60ef70b6a8b131626304694&as=trafficpark&av=0&ax=1&gdpr=%7BGDPR%7D&gdpr_consent=%7BGDPR_CONSENT%7D&p=product&prid=IDPRODUIT&ref=PAGE&w=doppelherz.pl&refdoc=&selfref=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus
Requested by
Host: p.gsitrix.com
URL: https://p.gsitrix.com/page/?a=60ef70b6a8b131626304694&p=product&prid={IDPRODUIT}&av=0&as=trafficpark&ax=1&w=doppelherz.pl&gdpr={GDPR}&gdpr_consent={GDPR_CONSENT}&ref={PAGE}
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_128_GCM
Server
85.195.73.74 Frankfurt am Main, Germany, ASN29066 (VELIANET-AS velia.net Internetdienste GmbH, DE),
Reverse DNS
Software
nginx/1.16.1 / PHP/7.4.6
Resource Hash
150c271bc18110a455847c8a1a9977d49c500e5303bc63ed79af11ef688ad1c6

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

Transfer-Encoding
chunked
Cache-Control
no-store, no-cache, must-revalidate
Pragma
no-cache
Connection
keep-alive
Expires
Sat, 13 Jun 1992 00:00:00 GMT
P3P
CP="NOI DEVa TAIa OUR BUS UNI"
Date
Wed, 16 Sep 2026 06:45:49 GMT
Content-Type
application/x-javascript; charset=utf-8
X-Powered-By
PHP/7.4.6
Server
nginx/1.16.1
POST
H2
200
ax.php Show response
p.gsitrix.com/js/ Frame D8C3
0
138 B
276ms
146ms
XHR
text/plain
85.195.93.95
VELIANET-AS velia...
General
Full URL
https://p.gsitrix.com/js/ax.php
Requested by
Host: p.gsitrix.com
URL: https://p.gsitrix.com/page/?a=60ef70b6a8b131626304694&p=product&prid={IDPRODUIT}&av=0&as=trafficpark&ax=1&w=doppelherz.pl&gdpr={GDPR}&gdpr_consent={GDPR_CONSENT}&ref={PAGE}
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
85.195.93.95 Frankfurt am Main, Germany, ASN29066 (VELIANET-AS velia.net Internetdienste GmbH, DE),
Reverse DNS
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
application/x-www-form-urlencoded
sec-ch-ua-mobile
?0

Response headers

access-control-allow-headers
*
access-control-allow-origin
https://sklep.doppelherz.pl
content-length
0
date
Wed, 16 Sep 2026 06:45:49 GMT
access-control-allow-credentials
true
access-control-allow-methods
*
GET
H2
200
pet.php Show response
p.gsitrix.com/tk/ Frame D8C3
280 B
353 B
46ms
46ms
Script
application/javascript
85.195.93.95
VELIANET-AS velia...
General
Full URL
https://p.gsitrix.com/tk/pet.php
Requested by
Host: p.gsitrix.com
URL: https://p.gsitrix.com/page/?a=60ef70b6a8b131626304694&p=product&prid={IDPRODUIT}&av=0&as=trafficpark&ax=1&w=doppelherz.pl&gdpr={GDPR}&gdpr_consent={GDPR_CONSENT}&ref={PAGE}
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
85.195.93.95 Frankfurt am Main, Germany, ASN29066 (VELIANET-AS velia.net Internetdienste GmbH, DE),
Reverse DNS
Software
/
Resource Hash
c23d306bfb0f833c5d7c58720d44bbdb2edf785ab31d7ddf709628b0ed1e60d9

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
public
etag
365b940481879a53942c944f
access-control-allow-credentials
true
access-control-allow-methods
*
access-control-allow-origin
*
content-length
280
date
Wed, 16 Sep 2026 06:45:49 GMT
content-type
application/javascript
access-control-allow-headers
*
GET
H2
200
us6mch Show response
ban.2trk.info/rtb/p0n/ Frame 0453
Redirect Chain
  • https://cm.g.doubleclick.net/pixel?google_nid=preciso_srl&google_ula=6490516189&google_cm&cok15=pne_dpp_pl&cnty15=POL&t=4&ProgramName=DOPPELHERZ_PL&AudienceId=3987&CampaignId=63729&Referrer=https%3...
  • https://ban.2trk.info/rtb/p0n/us6mch?id=p_srl&cok15=pne_dpp_pl&cnty15=POL&t=4&ProgramName=DOPPELHERZ_PL&AudienceId=3987&CampaignId=63729&Referrer=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-syst...
88 B
1 KB
176ms
89ms
Document
text/html
104.18.2.89
Cloudflare
General
Full URL
https://ban.2trk.info/rtb/p0n/us6mch?id=p_srl&cok15=pne_dpp_pl&cnty15=POL&t=4&ProgramName=DOPPELHERZ_PL&AudienceId=3987&CampaignId=63729&Referrer=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&ProductId=412&ProductCategoryList=Doppelherz%20system&PageType=product&Browsercheck=true&gdpr=0&gdpr_pd=0&a15=false&dw15=false&google_gid=CAESEPrRQqX8UJgcOMF4Kmq2HUw&google_cver=1&google_ula=6490516189,0
Requested by
Host: cdn.preciso.net
URL: https://cdn.preciso.net/aud/clientjs/3987.js?
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.18.2.89 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
e77ddf6d872e25c6859182b24337ab033d70f34756d5d636c8bd6e8531a6be4d
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://sklep.doppelherz.pl/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

cache-control
no-cache, no-store, max-age=0, must-revalidate, no-transform
cf-cache-status
DYNAMIC
cf-ray
a3bde919ac34b607-WAW
content-length
88
content-type
text/html;charset=ISO-8859-1
date
Wed, 16 Sep 2026 06:45:49 GMT
expires
0
pragma
no-cache
referrer-policy
unsafe-url
server
cloudflare
vary
Origin,Access-Control-Request-Method,Access-Control-Request-Headers
via
1.1 google
x-content-type-options
nosniff
x-xss-protection
0

Redirect headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cache-control
no-cache, must-revalidate
content-length
692
content-type
text/html; charset=UTF-8
cross-origin-resource-policy
cross-origin
date
Wed, 16 Sep 2026 06:45:49 GMT
expires
Fri, 01 Jan 1990 00:00:00 GMT
location
https://ban.2trk.info/rtb/p0n/us6mch?id=p_srl&cok15=pne_dpp_pl&cnty15=POL&t=4&ProgramName=DOPPELHERZ_PL&AudienceId=3987&CampaignId=63729&Referrer=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&ProductId=412&ProductCategoryList=Doppelherz%20system&PageType=product&Browsercheck=true&gdpr=0&gdpr_pd=0&a15=false&dw15=false&google_gid=CAESEPrRQqX8UJgcOMF4Kmq2HUw&google_cver=1&google_ula=6490516189,0
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
pragma
no-cache
server
HTTP server (unknown)
x-xss-protection
0
GET

product
ban.2trk.info/rtb/p2/analytics/DOPPELHERZ_PL/
0
0


POST
H3
200
tr Show response
rtg.wewomedia.com/
0
13 B
51ms
49ms
XHR
text/plain
34.102.157.203
Google LLC
General
Full URL
https://rtg.wewomedia.com/tr
Requested by
Host: rtg.wewomedia.com
URL: https://rtg.wewomedia.com/track/code.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
34.102.157.203 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
203.157.102.34.bc.googleusercontent.com
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
application/json
sec-ch-ua-mobile
?0

Response headers

access-control-expose-headers
Content-Length
access-control-allow-credentials
true
via
1.1 google
access-control-allow-origin
*
alt-svc
h3=":443"; ma=2592000
content-length
0
date
Wed, 16 Sep 2026 06:45:49 GMT
vary
Accept-Encoding
OPTIONS
H3
204
tr
rtg.wewomedia.com/ Frame
0
0
102ms
51ms
Preflight
34.102.157.203
Google LLC
General
Full URL
https://rtg.wewomedia.com/tr
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
34.102.157.203 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
203.157.102.34.bc.googleusercontent.com
Software
/
Resource Hash

Request headers

Accept
*/*
Access-Control-Request-Headers
content-type
Access-Control-Request-Method
POST
Origin
https://sklep.doppelherz.pl
Sec-Fetch-Mode
cors
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36

Response headers

access-control-allow-credentials
true
access-control-allow-headers
Origin,Content-Type
access-control-allow-methods
POST,GET,OPTIONS
access-control-allow-origin
*
alt-svc
h3=":443"; ma=2592000
date
Wed, 16 Sep 2026 06:45:49 GMT
vary
Accept-Encoding
via
1.1 google
GET
H/1.1
200
OK
s Show response
altopd.com/
8 KB
3 KB
51ms
51ms
Script
text/javascript
18.197.44.30
Amazon.com
General
Full URL
https://altopd.com/s?s=39149445&h=sklep.doppelherz.pl
Requested by
Host: altopd.com
URL: https://altopd.com/lod
Protocol
HTTP/1.1
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
18.197.44.30 Frankfurt am Main, Germany, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-18-197-44-30.eu-central-1.compute.amazonaws.com
Software
nginx /
Resource Hash
14e5b2f4cd21cdeabde3b642066afda4d92b8347b9d78c64d414bb3cec5bc2e4

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

Transfer-Encoding
chunked
Cache-Control
no-store, no-cache, private
Content-Encoding
gzip
Pragma
no-cache
Connection
keep-alive
Date
Wed, 16 Sep 2026 06:45:49 GMT
Content-Type
text/javascript
Server
nginx
POST
H2
200
serve42.php Show response
octaadsmedia.com/
0
402 B
338ms
191ms
Fetch
text/html
92.113.16.12
AS-HOSTINGER Host...
General
Full URL
https://octaadsmedia.com/serve42.php
Requested by
Host: sklep.doppelherz.pl
URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
92.113.16.12 Frankfurt am Main, Germany, ASN47583 (AS-HOSTINGER Hostinger International Limited, CY),
Reverse DNS
Software
hcdn / PHP/8.5.5
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

x-hcdn-request-id
b2ccddfa4dbc8597047538b41351e75d-fra-edge3
x-hcdn-upstream-rt
0.123
content-encoding
zstd
access-control-allow-methods
POST, OPTIONS
alt-svc
h3=":443"; ma=86400
date
Wed, 16 Sep 2026 06:45:49 GMT
x-hcdn-cache-status
DYNAMIC
content-type
text/html; charset=UTF-8
vary
Accept-Encoding
platform
hostinger
access-control-allow-headers
Content-Type
content-security-policy
upgrade-insecure-requests
access-control-allow-origin
*
x-powered-by
PHP/8.5.5
server
hcdn
panel
hpanel
GET
H3
200
p.js Show response
my.rtmark.net/
697 B
741 B
85ms
53ms
Script
text/javascript
104.18.41.22
Cloudflare
General
Full URL
https://my.rtmark.net/p.js?f=sync&lr=1&partner=f0532606cf524890c5fe2336b7bae95182f8d83cba419c8282f93d0a320d8561
Requested by
Host: static-cdn.trackier.com
URL: https://static-cdn.trackier.com/rtg/6a743395c3538afa3704b77a.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.18.41.22 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
2aecce5f3002d9b52dda7dee72c341653d072a7d8af22121bf518532ac542249
Security Headers
Name Value
Strict-Transport-Security max-age=1
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

access-control-expose-headers
Authorization
content-encoding
gzip
cf-cache-status
DYNAMIC
access-control-allow-methods
POST, GET, OPTIONS, PUT, DELETE
x-content-type-options
nosniff
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Wed, 16 Sep 2026 06:45:49 GMT
content-type
text/javascript
priority
u=3,i=?0
access-control-allow-headers
Accept, Content-Type, Content-Length, Accept-Encoding, Authorization,X-CSRF-Token
strict-transport-security
max-age=1
timing-allow-origin
*
access-control-allow-credentials
true
cf-ray
a3bde918fd5b88e8-WAW
access-control-allow-origin
*
server
cloudflare
GET
H3
200
collector Show response
mediaconvertly.com/
0
493 B
151ms
151ms
Script
text/javascript
104.21.10.19
Cloudflare
General
Full URL
https://mediaconvertly.com/collector?uid=c4b2gxg1789541149549&sid=wckkmuh1789541149549&url=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&ref=&ifr=0&mob=0&scr=1600x1200&lang=pl-PL&tz=Europe%2FWarsaw&tzof=-120&id=ZQK-JIAO2K&ts=1789541149550
Requested by
Host: mediaconvertly.com
URL: https://mediaconvertly.com/src/resource/js?tag=ZQK-JIAO2K
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.21.10.19 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-store, no-cache, must-revalidate, post-check=0, pre-check=0
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
cf-cache-status
DYNAMIC
pragma
no-cache
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=%2FyVGuhils6c2amTIAeV9b%2FAf8TsZn8REohBy7f%2FY4Ou%2B3CPEpv2IBX8JQIGwEXClRISqN%2BEIoVbisfzwkbyjpV%2FU4QzLARtnuDtVfjNJghs0yMecDCUYbZPKth6oZ2XCIBJe4Ew%3D"}]}
cf-ray
a3bde918caecbfe9-WAW
expires
0
server-timing
cfExtPri
alt-svc
h3=":443"; ma=86400
content-length
0
date
Wed, 16 Sep 2026 06:45:49 GMT
content-type
text/javascript
server
cloudflare
priority
u=3,i=?0
OPTIONS
H3
204
events
afftrack.pro/api/v1/ Frame
0
0
165ms
132ms
Preflight
188.114.96.3
Cloudflare
General
Full URL
https://afftrack.pro/api/v1/events
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
188.114.96.3 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare / Express
Resource Hash

Request headers

Accept
*/*
Access-Control-Request-Headers
content-type
Access-Control-Request-Method
POST
Origin
https://sklep.doppelherz.pl
Sec-Fetch-Mode
cors
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36

Response headers

access-control-allow-credentials
true
access-control-allow-headers
Content-Type,Authorization,X-API-Key
access-control-allow-methods
GET,POST,PUT,PATCH,DELETE,OPTIONS
access-control-allow-origin
https://sklep.doppelherz.pl
alt-svc
h3=":443"; ma=86400
cf-cache-status
DYNAMIC
cf-ray
a3bde918f9a5b6b9-WAW
date
Wed, 16 Sep 2026 06:45:49 GMT
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
priority
u=4,i
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=z14xh25d0JkzWVEQOGvVRljAvho6HgCEBzI1HCXbalrW5YN%2Bnpw%2BGOsjBvmkOOCsNfyjnPk5%2Fbs0YVgW%2F19C%2BgbM9JVGJOp5ALEwASiqdw%2FrGQ7FDsvH1p5c8E8OwIY%3D"}]}
server
cloudflare
server-timing
cfExtPri
vary
Origin
x-powered-by
Express
POST
H3
201
events
afftrack.pro/api/v1/
11 B
526 B
136ms
135ms
Ping
application/json
188.114.96.3
Cloudflare
General
Full URL
https://afftrack.pro/api/v1/events
Requested by
Host: afftrack.pro
URL: https://afftrack.pro/api/v1/script/c028ec8c-2f80-4c3b-b988-e72fbfa2b3e8/beacon-apstje.js?p=c028ec8c-2f80-4c3b-b988-e72fbfa2b3e8
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
188.114.96.3 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare / Express
Resource Hash
4062edaf750fb8074e7e83e0c9028c94e32468a8b6f1614774328ef045150f93

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
application/json
sec-ch-ua-mobile
?0

Response headers

cf-cache-status
DYNAMIC
etag
W/"b-Ai2R8hgEarLmHKwesT1qcY913ys"
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=UEzOrM%2FU69v%2FaMPnJ9CzkuAdcUZdu9tOFlaK1JsT4tOWhY%2FYSFj33xUxVDjGuKswUpw%2BtjCO2BxsRoqdL4g9qmvGXRb8rrQegiJESWzQwaIPndNPpu6m3M194bLCSj0%3D"}]}
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Wed, 16 Sep 2026 06:45:49 GMT
content-type
application/json; charset=utf-8
vary
Origin
priority
u=4,i
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
access-control-allow-credentials
true
cf-ray
a3bde919de43714a-WAW
access-control-allow-origin
https://sklep.doppelherz.pl
content-length
11
x-powered-by
Express
server
cloudflare
GET
H3
200
beacon.js Show response
afftrack.pro/api/v1/script/c028ec8c-2f80-4c3b-b988-e72fbfa2b3e8/
9 KB
4 KB
353ms
352ms
Script
application/javascript
188.114.96.3
Cloudflare
General
Full URL
https://afftrack.pro/api/v1/script/c028ec8c-2f80-4c3b-b988-e72fbfa2b3e8/beacon.js?p=c028ec8c-2f80-4c3b-b988-e72fbfa2b3e8&f=aHR0cHM6Ly9za2xlcC5kb3BwZWxoZXJ6LnBsL2RvcHBlbGhlcnotc3lzdGVtLWtvbGxhZ2VuLTExMDAwLXBsdXM%3D&g=67a84a7eb2aeacb8478779ec656c4071&r=
Requested by
Host: afftrack.pro
URL: https://afftrack.pro/api/v1/script/c028ec8c-2f80-4c3b-b988-e72fbfa2b3e8/beacon-apstje.js?p=c028ec8c-2f80-4c3b-b988-e72fbfa2b3e8
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
188.114.96.3 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare / Express
Resource Hash
a88edde0efac58f74191dd77dd33b4e72416c28e686c2bcaa6683959a7e15df1

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

content-encoding
zstd
cf-cache-status
MISS
etag
W/"25b9-8W3KWjnkxOaz0yCdUTtzP2VKGSk"
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=gfd98GKsC8t%2Bu2ntbQ2AA%2F%2BjEaGxzI%2B0%2BjPTV6NM%2Beey054YEInA68cVmee4rG%2BwCgK65uZtxAFZsVyxor6MaVAOw%2FidoVaQ5LgTJ%2BHmOd4fppdfArXnPmigDQlTiVY%3D"}]}
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Wed, 16 Sep 2026 06:45:49 GMT
content-type
application/javascript; charset=utf-8
vary
Origin
priority
u=3,i=?0
cache-control
public, max-age=14400
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
access-control-allow-credentials
true
cf-ray
a3bde918cc26714a-WAW
x-powered-by
Express
server
cloudflare
GET
H3
200
runtime.js Show response
afftrack.pro/api/v1/offer/
8 B
525 B
35ms
35ms
Script
application/javascript
188.114.96.3
Cloudflare
General
Full URL
https://afftrack.pro/api/v1/offer/runtime.js?h=sklep.doppelherz.pl
Requested by
Host: afftrack.pro
URL: https://afftrack.pro/api/v1/script/c028ec8c-2f80-4c3b-b988-e72fbfa2b3e8/beacon-apstje.js?p=c028ec8c-2f80-4c3b-b988-e72fbfa2b3e8
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
188.114.96.3 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare / Express
Resource Hash
78a7a3c1c34559fd5864aba01e7a1f20d6f881259c8b32e28cfa9d6b2801f35f

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cf-cache-status
HIT
etag
W/"8-SefW281xNzOBZqOpfanevMg2WEQ"
age
18
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=g2slHLxTo6Oi6zwrV1%2BpWmsUKZyKcbvExQVdV3R78X7j7aKLcVyURlBxg58vT42dvR%2FBj9MlSPiGLLyi0feJVrgvBNgHWhNrGq5weBlTSqaDFboxQs8KSUQnU%2FhKG%2Bg%3D"}]}
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Wed, 16 Sep 2026 06:45:49 GMT
content-type
application/javascript; charset=utf-8
vary
Origin
priority
u=3,i=?0
cache-control
public, max-age=14400
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
access-control-allow-credentials
true
cf-ray
a3bde918cc2e714a-WAW
accept-ranges
bytes
content-length
8
x-powered-by
Express
server
cloudflare
GET
H2
200
retar_js.php Show response
vu.adschoom.com/trafic/
8 B
361 B
63ms
62ms
Script
text/javascript
51.210.24.88
OVH OVH SAS
General
Full URL
https://vu.adschoom.com/trafic/retar_js.php?type=PRODUIT&boutique=Doppelherzpl&categorie_id=&produit_id=412&data=&transaction_id=0&transaction_amount=0&valid=1&rid_tt=&refer=https%3A//sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus&refer2=&shopf=false&random=444486834
Requested by
Host: vu.adschoom.com
URL: https://vu.adschoom.com/trafic/retar.php?boutique=Doppelherzpl&type=PRODUIT&produit_id=412&gdpr_consent=&topfr=https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus&topfr2=
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
51.210.24.88 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
ns3257326.ip-51-210-24.eu
Software
nginx/1.24.0 (Ubuntu) /
Resource Hash
45336bf2c27960347588ebaedc466e533d74cb661ed98b7d8b45c27a54e0e596

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

expires
Sun, 06 Sep 2026 06:45:49 GMT
cache-control
no-store, no-cache, must-revalidate, post-check=0, pre-check=0
date
Wed, 16 Sep 2026 06:45:49 GMT
pragma
no-cache
content-type
text/javascript;charset=UTF-8
server
nginx/1.24.0 (Ubuntu)
POST
H3
200
/ Show response
loopwidget.com/ret/
0
562 B
197ms
163ms
Fetch
188.114.97.3
Cloudflare
General
Full URL
https://loopwidget.com/ret/
Requested by
Host: loopwidget.com
URL: https://loopwidget.com/ret.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
188.114.97.3 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare / Express
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
application/x-www-form-urlencoded;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
cf-cache-status
DYNAMIC
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=alB7%2FqZ4TfzgqZhmbHjWKb2Hy9krNhIfyJ4cF6fX9KMqQmqNqDB8L09KKSEZ0wB%2FWrnzn9CAiHjf86x7jd1BelSQzupbITytwdIVDyNgqu6gFCd8QApKNxeTCM7FlRNX6A%3D%3D"}]}
cf-ray
a3bde9190db7b198-WAW
access-control-allow-origin
*
alt-svc
h3=":443"; ma=86400
content-length
0
server-timing
cfExtPri
date
Wed, 16 Sep 2026 06:45:49 GMT
x-powered-by
Express
server
cloudflare
priority
u=1,i
POST
H2
200
ax.php Show response
p.gsitrix.com/js/ Frame D8C3
0
16 B
100ms
99ms
XHR
text/plain
85.195.93.95
VELIANET-AS velia...
General
Full URL
https://p.gsitrix.com/js/ax.php
Requested by
Host: p.gsitrix.com
URL: https://p.gsitrix.com/page/?a=60ef70b6a8b131626304694&p=product&prid={IDPRODUIT}&av=0&as=trafficpark&ax=1&w=doppelherz.pl&gdpr={GDPR}&gdpr_consent={GDPR_CONSENT}&ref={PAGE}
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
85.195.93.95 Frankfurt am Main, Germany, ASN29066 (VELIANET-AS velia.net Internetdienste GmbH, DE),
Reverse DNS
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
application/x-www-form-urlencoded
sec-ch-ua-mobile
?0

Response headers

access-control-allow-headers
*
access-control-allow-origin
https://sklep.doppelherz.pl
content-length
0
date
Wed, 16 Sep 2026 06:45:49 GMT
access-control-allow-credentials
true
access-control-allow-methods
*
GET
H/1.1
200
OK
p Show response
altopd.com/
0
391 B
54ms
54ms
Script
text/javascript
18.197.44.30
Amazon.com
General
Full URL
https://altopd.com/p?s=49864993&h=sklep.doppelherz.pl&body=%7B%22r%22%3A0.09163639128434328%2C%22id%22%3A%22HybS7%22%2C%22ref%22%3A%22%22%2C%22uri%22%3A%22https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus%22%2C%22j%22%3Afalse%2C%22o%22%3A0%2C%22d%22%3Afalse%2C%22utm%22%3A%7B%22adid%22%3A%22178954114967954%22%7D%2C%22utm2%22%3A%7B%7D%2C%22order%22%3Anull%7D
Requested by
Host: altopd.com
URL: https://altopd.com/s?s=39149445&h=sklep.doppelherz.pl
Protocol
HTTP/1.1
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
18.197.44.30 Frankfurt am Main, Germany, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-18-197-44-30.eu-central-1.compute.amazonaws.com
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

Transfer-Encoding
chunked
Cache-Control
no-store, no-cache, private
Content-Encoding
gzip
Pragma
no-cache
Connection
keep-alive
Date
Wed, 16 Sep 2026 06:45:49 GMT
Content-Type
text/javascript
Server
nginx
POST
H3
201
decision Show response
afftrack.pro/api/v1/
58 B
581 B
134ms
133ms
Fetch
application/json
188.114.96.3
Cloudflare
General
Full URL
https://afftrack.pro/api/v1/decision
Requested by
Host: afftrack.pro
URL: https://afftrack.pro/api/v1/script/c028ec8c-2f80-4c3b-b988-e72fbfa2b3e8/beacon.js?p=c028ec8c-2f80-4c3b-b988-e72fbfa2b3e8&f=aHR0cHM6Ly9za2xlcC5kb3BwZWxoZXJ6LnBsL2RvcHBlbGhlcnotc3lzdGVtLWtvbGxhZ2VuLTExMDAwLXBsdXM%3D&g=67a84a7eb2aeacb8478779ec656c4071&r=
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
188.114.96.3 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare / Express
Resource Hash
22f4aadb4161427bd826844d8682e474361a17c13a15271b44b68a1ec62324db

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
application/json
sec-ch-ua-mobile
?0

Response headers

cf-cache-status
DYNAMIC
etag
W/"3a-qlX+dduYBggxGTuU3cPUY8CwJVk"
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=LnWdobm0GP9rMK8ihIvt0SizhSkORgLMpjrutrKgWLmG%2FJSYnINC%2B0o%2BQaNHU63jbzyy%2BaMJu7%2Fta0HUQ7NhWPHBvpxw5tRMffQSiIV%2BFGtL3i%2BMcNjtl5OSXXIQvqs%3D"}]}
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Wed, 16 Sep 2026 06:45:50 GMT
content-type
application/json; charset=utf-8
vary
Origin
priority
u=1,i
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
access-control-allow-credentials
true
cf-ray
a3bde91c589cb6b9-WAW
access-control-allow-origin
https://sklep.doppelherz.pl
content-length
58
x-powered-by
Express
server
cloudflare
OPTIONS
H3
204
decision
afftrack.pro/api/v1/ Frame
0
0
132ms
132ms
Preflight
188.114.96.3
Cloudflare
General
Full URL
https://afftrack.pro/api/v1/decision
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
188.114.96.3 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare / Express
Resource Hash

Request headers

Accept
*/*
Access-Control-Request-Headers
content-type
Access-Control-Request-Method
POST
Origin
https://sklep.doppelherz.pl
Sec-Fetch-Mode
cors
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36

Response headers

access-control-allow-credentials
true
access-control-allow-headers
Content-Type,Authorization,X-API-Key
access-control-allow-methods
GET,POST,PUT,PATCH,DELETE,OPTIONS
access-control-allow-origin
https://sklep.doppelherz.pl
alt-svc
h3=":443"; ma=86400
cf-cache-status
DYNAMIC
cf-ray
a3bde91b8f3eb6b9-WAW
date
Wed, 16 Sep 2026 06:45:50 GMT
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
priority
u=1,i
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=vH7Z6MtvIeKgXsMUYlQqkKKF%2B10O8WrIB2H%2Bz2rnu866m1vgkmk1Uj%2FxwMrtjgge7V1zT7KIA6qTEbU2HoXsx5qB42vJN1hZmu8wAKb3E7Myzrmjrq5EPn6voQDU2OY%3D"}]}
server
cloudflare
server-timing
cfExtPri
vary
Origin
x-powered-by
Express
POST
H/1.1
200
OK
/ Show response
firehose.eu-west-1.amazonaws.com/
299 B
738 B
118ms
117ms
XHR
application/x-amz-json-1.1
99.80.34.227
Amazon.com
General
Full URL
https://firehose.eu-west-1.amazonaws.com/
Requested by
Host: js.smct.io
URL: https://js.smct.io/v7.14.0-beta.20/tag-v7.14.0-beta.20.js
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_128_GCM
Server
99.80.34.227 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-99-80-34-227.eu-west-1.compute.amazonaws.com
Software
/
Resource Hash
69a94e631a810ca34a04492e865f1088b16a1863bddd838f12de9e85844485d1

Request headers

sec-ch-ua-platform
"Linux"
Authorization
AWS4-HMAC-SHA256 Credential=ASIAX2DUJRE4YGKK3LAD/20260916/eu-west-1/firehose/aws4_request, SignedHeaders=host;x-amz-date;x-amz-security-token;x-amz-target, Signature=d47514727cf0b46538553bc813a0b34db24f7c434d9083e319913dc68783589c
Referer
https://sklep.doppelherz.pl/
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
x-amz-security-token
IQoJb3JpZ2luX2VjEEcaCWV1LXdlc3QtMSJGMEQCIB113puMDL8jjvK++1+sh41UHbpa0v5tWZeZ5Wb9qp8QAiAjZd+DAtf5Hec3z8v6LYcgqJhsmvJUAt3NFva90wrO1yqvBQgQEAQaDDUzNzExNDgwNjU4NSIM1m5rXuifLzGzHrO2KowFfzko/pax4GipGsLl9Hg3tzxfFYNzvmlebGsVXA8jTWFCw4D+wZ9MNeAqaE8jTsqMSsXRuERoXbnYJovHaS1yjrXz5rgVZqDuxUOMPSZpMIEm09Gbio+7FZp2tOBdR2fOOtG2veM/lqBDh/zsG/Qgr769WneOIXTbeiCYfc+wOeKGVxMJI7JC/oBsYQhMS7GTlrSbwGXUjLJ75xkEDAhuGF7Hv56YBXZCYM08l2vMItKXW0mCjpwjgAVC6qBqGJ6P8RHlC8vHRSWH+Py5igxCeVS+1Qqa+VvoizQrruxTovvqZJdjwRvuoMTex1Eak4YoP4h24V+7bybttfJVNTegDo3h1oNk5xnSIO/yhzGGYbjUDTb6PqLHa/Jypi7jBWa2KiA7k0X9l26EI+hrZTlQ5OysBC75bTHykPBAd4NuAopRoI4efMkoJm9xTjXhOuo10iwoa5d/OP3CUqonOsM4ksKXM2ghp4sUplNmsvfmlXAuk8pZC2V4/SWMRz1e9dTV/FxmV3fZJl22cIeY5KW2PcZZM4hrmluVa8JRIMxkAMwFE8iZTxZ+PFL4wi4yggA9zWxVkpSwVbFuSWC3LXpGJW1DaWyIzk0oxz5FEeYMBA+qj2il9spWhB7oDNyn7cFFFGhv2pD6WYbFstKvYCZIryLH5aDAlB4SGuUnxov+5l9mrPNSwFyUAjKZvSfdZO1pgZE5QW0cIAgnzzFE2pzWsSjQORfhgTA/NLvQj1OXh64GLcUtQW4fcs8gIk2rWJbPef5D/FQ7JR4Dq60tavyAFZ5cA8rKbAnbvSB1JX0ZC7Qev3CdgL+9szraiLjZU3j2Emn14rg/TsPnvvIFefPdfbWC/oYrltC6zoWIYTCb9qjVBjreApKZ6oKPegnNEEAHd/7qMTf8YM+JaF2phSWHdGfiNWc9EAxRtzO++xiLsMxncAH2SWFjG2QaSf38CnKPQBThvX/UvtTHTuZaN5G+1L9rUqszrRuPSLrrRwrufNh01BzDXrGpsOBrKeHQ6z65NV87ewyfzqIxqii1nt4QAhi3ktWxNC1e1TFib+R2g5Gu9JH07yad34qHbVcDfHx9el2QL3bt2LYf6EajMTiGwdmczaw0gOmG3TzU0TrkGR9VqDtVCf/yKjxu3/K5lFxXzVJWk+NO58GvWP+8grurKXrzSoVbMZylm8ITfi3OHoJQOtmmjv+zj0lr1k1csnR1e4JqnqftRswbmwUS9oDs1J/TQfXnrigQq1IW6ioztPcnpqMa0s9VO8XC57m/L8vyYCCrXUw2Esp7J4Go/STgNtKNqvIfGMM6nArgzuqB7BceJNO+qdQ2CZMH+I9l9u/Dia8T
x-amz-date
20260916T064549Z
x-amz-target
Firehose_20150804.PutRecordBatch
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Content-Type
application/x-amz-json-1.1

Response headers

Access-Control-Expose-Headers
x-amz-request-id,x-amz-id-2,x-amzn-RequestId,x-amzn-ErrorType,x-amzn-ErrorMessage,Date
Content-Encoding
gzip
x-amzn-RequestId
f3f511cf-c01f-206b-90d1-2c91b92c2f0c
Access-Control-Allow-Origin
*
Content-Length
278
Date
Wed, 16 Sep 2026 06:45:50 GMT
Content-Type
application/x-amz-json-1.1
x-amz-id-2
YdSHyGDKYycYmBfcjTaFmzP/EpHXV1h7g0yHt9W4e+qbgKSEHDoxdwE15FD615lBEVSc02J3jJGreO3JcrOFEqxHrg8ss9Y1
GET
H3
200
img.gif
my.rtmark.net/
43 B
383 B
56ms
56ms
Image
image/gif
104.18.41.22
Cloudflare
General
Full URL
https://my.rtmark.net/img.gif?f=sync&partner=f0532606cf524890c5fe2336b7bae95182f8d83cba419c8282f93d0a320d8561&ttl=&rurl=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.18.41.22 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
4e0705327480ad2323cb03d9c450ffcae4a98bf3a5382fa0c7882145ed620e49
Security Headers
Name Value
Strict-Transport-Security max-age=1
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

access-control-expose-headers
Authorization
cf-cache-status
DYNAMIC
access-control-allow-methods
POST, GET, OPTIONS, PUT, DELETE
x-content-type-options
nosniff
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Wed, 16 Sep 2026 06:45:50 GMT
content-type
image/gif
priority
u=3,i
access-control-allow-headers
Accept, Content-Type, Content-Length, Accept-Encoding, Authorization,X-CSRF-Token
strict-transport-security
max-age=1
timing-allow-origin
*
access-control-allow-credentials
true
cf-ray
a3bde91cbdcb88e8-WAW
access-control-allow-origin
*
content-length
43
server
cloudflare
POST
H2
200
ax.php Show response
p.gsitrix.com/js/ Frame D8C3
0
39 B
115ms
113ms
XHR
text/plain
85.195.93.95
VELIANET-AS velia...
General
Full URL
https://p.gsitrix.com/js/ax.php
Requested by
Host: p.gsitrix.com
URL: https://p.gsitrix.com/page/?a=60ef70b6a8b131626304694&p=product&prid={IDPRODUIT}&av=0&as=trafficpark&ax=1&w=doppelherz.pl&gdpr={GDPR}&gdpr_consent={GDPR_CONSENT}&ref={PAGE}
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
85.195.93.95 Frankfurt am Main, Germany, ASN29066 (VELIANET-AS velia.net Internetdienste GmbH, DE),
Reverse DNS
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
application/x-www-form-urlencoded
sec-ch-ua-mobile
?0

Response headers

access-control-allow-headers
*
access-control-allow-origin
https://sklep.doppelherz.pl
content-length
0
date
Wed, 16 Sep 2026 06:45:50 GMT
access-control-allow-credentials
true
access-control-allow-methods
*
POST
H3
201
events
afftrack.pro/api/v1/
11 B
525 B
133ms
132ms
Ping
application/json
188.114.96.3
Cloudflare
General
Full URL
https://afftrack.pro/api/v1/events
Requested by
Host: afftrack.pro
URL: https://afftrack.pro/api/v1/script/c028ec8c-2f80-4c3b-b988-e72fbfa2b3e8/beacon.js?p=c028ec8c-2f80-4c3b-b988-e72fbfa2b3e8&f=aHR0cHM6Ly9za2xlcC5kb3BwZWxoZXJ6LnBsL2RvcHBlbGhlcnotc3lzdGVtLWtvbGxhZ2VuLTExMDAwLXBsdXM%3D&g=67a84a7eb2aeacb8478779ec656c4071&r=
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
188.114.96.3 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare / Express
Resource Hash
4062edaf750fb8074e7e83e0c9028c94e32468a8b6f1614774328ef045150f93

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
application/json
sec-ch-ua-mobile
?0

Response headers

cf-cache-status
DYNAMIC
etag
W/"b-Ai2R8hgEarLmHKwesT1qcY913ys"
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=p6hagpUojTWY20ozU3%2BNz%2FradWtSXGU1jNkL%2FATmpSX6CjC36qg1oFcXxzTuCuo3Mw8OPyNDF2o%2BCqtMjmfu5jhTPXdax1QDCebB5osvsdZMvpDxdeHhhL5LBLT57HA%3D"}]}
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Wed, 16 Sep 2026 06:45:50 GMT
content-type
application/json; charset=utf-8
vary
Origin
priority
u=4,i
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
access-control-allow-credentials
true
cf-ray
a3bde91d2c72714a-WAW
access-control-allow-origin
https://sklep.doppelherz.pl
content-length
11
x-powered-by
Express
server
cloudflare
POST
H3
204
collect
region1.google-analytics.com/g/
0
0
47ms
47ms
Fetch
text/plain
216.239.32.36
Google LLC
General
Full URL
https://region1.google-analytics.com/g/collect?v=2&tid=G-WK4E7DG3RJ&gtm=45je69f0h2v9185103690za200zd9185103690&_p=1789541144744&gcs=G100&gcd=13p3p3p2p5l1&npa=1&dma_cps=-&dma=1&cid=904344215.1789541146&frm=0&ngs=1&pscdl=denied&rcb=15&sr=1600x1200&uaa=x86&uab=64&uafvl=Chromium%3B153.0.8010.36%7CGoogle%2520Chrome%3B153.0.8010.36%7CNot_A%2520Brand%3B8.0.0.0&uam=&uamb=0&uap=Linux&uapv=&uaw=0&ul=pl-pl&_s=2&tag_exp=115616985~115938465~115938469~118897920~118897930~120213116~120385423~120469145~120469153&cu=PLN&sid=1789541145&sct=1&seg=0&dl=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&dt=Doppelherz%20system%20Kollagen%2011.000%20PLUS%20%7C%2030%20ampu%C5%82ek%20-%20sklep%20Doppelherz&en=view_item&_ee=1&pr1=nmDoppelherz%C2%AE%20system%20KOLLAGEN%2011.000%20PLUS%2C%2030%20ampu%C5%82ek%20po%2025ml~id412~brQueisser%20Pharma~caDoppelherz%20system~va~ln~lpNaN~pr122.7~k0currency~v0PLN~qt1&epn.value=122.7&_et=2&tfd=6757
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtag/js?id=G-WK4E7DG3RJ&l=dataLayer
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
216.239.32.36 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
Golfe2 /
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, no-store, must-revalidate
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
content-security-policy-report-only
script-src 'none'; form-action 'none'; frame-src 'none'; report-uri https://csp.withgoogle.com/csp/scaffolding/ascnsrsggc:139:0
report-to
{"group":"ascnsrsggc:139:0","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/scaffolding/ascnsrsggc:139:0"}],}
expires
Fri, 01 Jan 1990 00:00:00 GMT
access-control-allow-origin
https://sklep.doppelherz.pl
cross-origin-opener-policy-report-only
same-origin; report-to=ascnsrsggc:139:0
content-length
0
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 16 Sep 2026 06:45:50 GMT
content-type
text/plain
server
Golfe2
POST
H2
204
attest.php
vu.adschoom.com/trafic/
0
169 B
113ms
111ms
Ping
text/plain
51.210.24.88
OVH OVH SAS
General
Full URL
https://vu.adschoom.com/trafic/attest.php
Requested by
Host: vu.adschoom.com
URL: https://vu.adschoom.com/trafic/retar.php?boutique=Doppelherzpl&type=PRODUIT&produit_id=412&gdpr_consent=&topfr=https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus&topfr2=
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
51.210.24.88 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
ns3257326.ip-51-210-24.eu
Software
nginx/1.24.0 (Ubuntu) /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
Content-Type
application/x-www-form-urlencoded
sec-ch-ua-mobile
?0

Response headers

access-control-allow-headers
Content-Type
access-control-allow-origin
*
cache-control
no-store
date
Wed, 16 Sep 2026 06:45:51 GMT
server
nginx/1.24.0 (Ubuntu)
access-control-allow-methods
POST, GET, OPTIONS
POST
H3
204
collect
region1.google-analytics.com/g/
0
0
49ms
49ms
Fetch
text/plain
216.239.32.36
Google LLC
General
Full URL
https://region1.google-analytics.com/g/collect?v=2&tid=G-03LP30MEMG&gtm=45je69e1v871169519z8865320812za20gzb865320812zd865320812&_p=1789541144744&gcs=G100&gcd=13q3q3q2q5l1&npa=1&dma_cps=-&dma=1&_eu=AAAAAGAC&cid=904344215.1789541146&frm=0&pscdl=denied&rcb=1&sr=1600x1200&uaa=x86&uab=64&uafvl=Chromium%3B153.0.8010.36%7CGoogle%2520Chrome%3B153.0.8010.36%7CNot_A%2520Brand%3B8.0.0.0&uam=&uamb=0&uap=Linux&uapv=&uaw=0&ul=pl-pl&gaf=2&_s=2&tag_exp=115616985~115938465~115938468~118897920~118897930~120213116~120385423~120469145~120469153&cu=PLN&sid=1789541146&sct=1&seg=0&dl=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus&dt=Doppelherz%20system%20Kollagen%2011.000%20PLUS%20%7C%2030%20ampu%C5%82ek%20-%20sklep%20Doppelherz&_tu=CA&en=view_item&pr1=nmDoppelherz%C2%AE%20system%20KOLLAGEN%2011.000%20PLUS%2C%2030%20ampu%C5%82ek%20po%2025ml~id412~brQueisser%20Pharma~caDoppelherz%20system~va~ln~lpNaN~pr122.7~k0currency~v0PLN~qt1&ep.content_group=sklep.doppelherz.pl&ep.custom_source=(direct)&ep.custom_medium=(none)&ep.custom_campaign=(not%20set)&epn.value=122.7&_et=4&tfd=7258
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtag/js?id=G-03LP30MEMG&cx=c&gtm=4e69e1
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
216.239.32.36 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
Golfe2 /
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://sklep.doppelherz.pl/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, no-store, must-revalidate
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
content-security-policy-report-only
script-src 'none'; form-action 'none'; frame-src 'none'; report-uri https://csp.withgoogle.com/csp/scaffolding/ascnsrsggc:139:0
report-to
{"group":"ascnsrsggc:139:0","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/scaffolding/ascnsrsggc:139:0"}],}
expires
Fri, 01 Jan 1990 00:00:00 GMT
access-control-allow-origin
https://sklep.doppelherz.pl
cross-origin-opener-policy-report-only
same-origin; report-to=ascnsrsggc:139:0
content-length
0
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 16 Sep 2026 06:45:51 GMT
content-type
text/plain
server
Golfe2
POST
H/1.1
200
OK
/ Show response
firehose.eu-west-1.amazonaws.com/
299 B
740 B
116ms
115ms
XHR
application/x-amz-json-1.1
99.80.34.227
Amazon.com
General
Full URL
https://firehose.eu-west-1.amazonaws.com/
Requested by
Host: js.smct.io
URL: https://js.smct.io/v7.14.0-beta.20/tag-v7.14.0-beta.20.js
Protocol
HTTP/1.1
Security
TLS 1.3, , AES_128_GCM
Server
99.80.34.227 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-99-80-34-227.eu-west-1.compute.amazonaws.com
Software
/
Resource Hash
fc6fe0e4ae32f0bc3654f2151b99224b763545e4ab6ff020e0c18d250c21c4c2

Request headers

sec-ch-ua-platform
"Linux"
Authorization
AWS4-HMAC-SHA256 Credential=ASIAX2DUJRE4YGKK3LAD/20260916/eu-west-1/firehose/aws4_request, SignedHeaders=host;x-amz-date;x-amz-security-token;x-amz-target, Signature=3dcea7c98209499459e679bfa9579c7e44556c1a082ae81d15e50466242cd5d9
Referer
https://sklep.doppelherz.pl/
sec-ch-ua
"Chromium";v="153", "Google Chrome";v="153", "Not_A Brand";v="8"
sec-ch-ua-mobile
?0
x-amz-security-token
IQoJb3JpZ2luX2VjEEcaCWV1LXdlc3QtMSJGMEQCIB113puMDL8jjvK++1+sh41UHbpa0v5tWZeZ5Wb9qp8QAiAjZd+DAtf5Hec3z8v6LYcgqJhsmvJUAt3NFva90wrO1yqvBQgQEAQaDDUzNzExNDgwNjU4NSIM1m5rXuifLzGzHrO2KowFfzko/pax4GipGsLl9Hg3tzxfFYNzvmlebGsVXA8jTWFCw4D+wZ9MNeAqaE8jTsqMSsXRuERoXbnYJovHaS1yjrXz5rgVZqDuxUOMPSZpMIEm09Gbio+7FZp2tOBdR2fOOtG2veM/lqBDh/zsG/Qgr769WneOIXTbeiCYfc+wOeKGVxMJI7JC/oBsYQhMS7GTlrSbwGXUjLJ75xkEDAhuGF7Hv56YBXZCYM08l2vMItKXW0mCjpwjgAVC6qBqGJ6P8RHlC8vHRSWH+Py5igxCeVS+1Qqa+VvoizQrruxTovvqZJdjwRvuoMTex1Eak4YoP4h24V+7bybttfJVNTegDo3h1oNk5xnSIO/yhzGGYbjUDTb6PqLHa/Jypi7jBWa2KiA7k0X9l26EI+hrZTlQ5OysBC75bTHykPBAd4NuAopRoI4efMkoJm9xTjXhOuo10iwoa5d/OP3CUqonOsM4ksKXM2ghp4sUplNmsvfmlXAuk8pZC2V4/SWMRz1e9dTV/FxmV3fZJl22cIeY5KW2PcZZM4hrmluVa8JRIMxkAMwFE8iZTxZ+PFL4wi4yggA9zWxVkpSwVbFuSWC3LXpGJW1DaWyIzk0oxz5FEeYMBA+qj2il9spWhB7oDNyn7cFFFGhv2pD6WYbFstKvYCZIryLH5aDAlB4SGuUnxov+5l9mrPNSwFyUAjKZvSfdZO1pgZE5QW0cIAgnzzFE2pzWsSjQORfhgTA/NLvQj1OXh64GLcUtQW4fcs8gIk2rWJbPef5D/FQ7JR4Dq60tavyAFZ5cA8rKbAnbvSB1JX0ZC7Qev3CdgL+9szraiLjZU3j2Emn14rg/TsPnvvIFefPdfbWC/oYrltC6zoWIYTCb9qjVBjreApKZ6oKPegnNEEAHd/7qMTf8YM+JaF2phSWHdGfiNWc9EAxRtzO++xiLsMxncAH2SWFjG2QaSf38CnKPQBThvX/UvtTHTuZaN5G+1L9rUqszrRuPSLrrRwrufNh01BzDXrGpsOBrKeHQ6z65NV87ewyfzqIxqii1nt4QAhi3ktWxNC1e1TFib+R2g5Gu9JH07yad34qHbVcDfHx9el2QL3bt2LYf6EajMTiGwdmczaw0gOmG3TzU0TrkGR9VqDtVCf/yKjxu3/K5lFxXzVJWk+NO58GvWP+8grurKXrzSoVbMZylm8ITfi3OHoJQOtmmjv+zj0lr1k1csnR1e4JqnqftRswbmwUS9oDs1J/TQfXnrigQq1IW6ioztPcnpqMa0s9VO8XC57m/L8vyYCCrXUw2Esp7J4Go/STgNtKNqvIfGMM6nArgzuqB7BceJNO+qdQ2CZMH+I9l9u/Dia8T
x-amz-date
20260916T064552Z
x-amz-target
Firehose_20150804.PutRecordBatch
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/153.0.0.0 Safari/537.36
Content-Type
application/x-amz-json-1.1

Response headers

Access-Control-Expose-Headers
x-amz-request-id,x-amz-id-2,x-amzn-RequestId,x-amzn-ErrorType,x-amzn-ErrorMessage,Date
Content-Encoding
gzip
x-amzn-RequestId
de2306c1-21c2-785a-bd07-3ba158f1773d
Access-Control-Allow-Origin
*
Content-Length
280
Date
Wed, 16 Sep 2026 06:45:52 GMT
Content-Type
application/x-amz-json-1.1
x-amz-id-2
Q1uxQMHkXihzOlmBOZeIpFwUISqk1msoTxgM+7vcN3Mcrrs761llRr5AKE4qs2LRwthxfMIUcRhsoHE2m80futqBFdEwbDVR

Failed requests

These URLs were requested, but there was no response received. You will also see them in the list above.

Domain
sklep.doppelherz.pl
URL
https://sklep.doppelherz.pl/upload/fonts/aestetico_regular.otf&display=swap
Domain
sklep.doppelherz.pl
URL
https://sklep.doppelherz.pl/upload/fonts/aestetico_semibold.otf&display=swap
Domain
hotinfo.maxserver.pl
URL
https://hotinfo.maxserver.pl/appHotbasket/script.php?shop=a96db86b9d7d6d7f128220325e99fe925c001520&m=1779714858
Domain
trustmate.io
URL
https://trustmate.io/images/widgets/badges/v2/pl/trusted.svg
Domain
trustmate.io
URL
https://trustmate.io/images/widgets/badges/v2/pl/trusted.svg
Domain
trustmate.io
URL
https://trustmate.io/images/widgets/badges/v2/pl/trusted.svg
Domain
trustmate.io
URL
https://trustmate.io/images/widgets/badges/v2/pl/trusted.svg
Domain
ssp.wp.pl
URL
https://ssp.wp.pl/v1/user_sync_status
Domain
ban.tangooserver.com
URL
https://ban.tangooserver.com/audit.aspx?token=DOPPELHERZ_AWI_PL&pagetype=product&t=1&ref=https%3a%2f%2fsklep.doppelherz.pl%2f
Domain
trustmate.io
URL
https://trustmate.io/images/widgets/badges/v2/pl/trusted.svg
Domain
secure.adnxs.com
URL
https://secure.adnxs.com/getuid?https://c1.adform.net/serving/cookie/match?party=3&id=$UID&redirect=1
Domain
match.contentexchange.me
URL
https://match.contentexchange.me/adform/5351721985196806187?redirect_url=https%3a%2f%2fc1.adform.net%2fserving%2fcookie%2fmatch%3fparty%3d1219
Domain
tags.fulllab.com.br
URL
https://tags.fulllab.com.br/scripts/ZQK-JIAO2K.js
Domain
rev.owltrack.com
URL
https://rev.owltrack.com/d/asyncjs.php
Domain
ban.tangooserver.com
URL
https://ban.tangooserver.com/audit.aspx?token=DOPPELHERZ_PL8879&pagetype=product&t=1&ref=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus
Domain
ban.2trk.info
URL
https://ban.2trk.info/rtb/p2/analytics/DOPPELHERZ_PL/product?t=1&ref=https%3A%2F%2Fsklep.doppelherz.pl%2Fdoppelherz-system-kollagen-11000-plus

Verdicts & Comments Add Verdict or Comment

268 JavaScript Window variables

These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.

object| 0 object| 1 object| 2 object| 3 object| 4 object| 5 object| 6 object| 7 object| 8 object| 9 object| preloader function| hidePreloader boolean| hasCache boolean| cssLoaded object| webpackJsonp function| $ function| jQuery object| html5 object| Modernizr function| yepnope object| fastdom object| regeneratorRuntime function| setImmediate function| clearImmediate function| _ function| gFormSubmit function| recaptchaRender object| customerPrivacy function| Shop function| _$ function| googleMapsAPICallback function| gm_authFailure function| $on function| $off function| $emit object| __core-js_shared__ object| core boolean| _babelPolyfill function| Hammer object| jQuery111308371321020135769 object| dataLayer function| _ceneo string| WphTrackObject function| wph object| frontAPI object| KWKUniJS string| _smswdomain object| Mustache function| FilterFakeSelect object| ___gcfg function| renderBadge string| url function| wph_ps object| content_types object| mamezi_product_boxes_data string| _smshop object| produkty_powiazane_data function| tmWidgetNode function| tmWidgetPlace object| UI object| tmWidgetUI function| trustMateLoadWidget object| related_products_titles function| lateScripts function| trustmateProductpage function| owlCarousels function| fvAddAgree function| mobileProductBelt function| bestProdGen function| addBestClass function| calculateBundleOriginalPrice function| toggleComments function| productDescNav function| fpCategoriesNav function| mobileFilter function| basketContain function| mobileStickyMenu function| mobileSort function| selectedFilters function| mobileCategorydesc function| joinedProdNav function| mobilePerks function| addInputButtons function| SliderMobileGallery function| addMenuItems boolean| _smbanners boolean| _smcustom object| mmzConfigs function| lozad function| Shortcode string| pluginName function| BoxProducts function| initScriptBoxy function| postInitBoxProducts object| addtobasket boolean| isGA4Active object| shopLayer object| shoper number| windowWidth string| DoofinderAppsObject function| doofinderApp object| gapi object| ___jsl object| ___gu function| initFrontRelatedProducts function| sortProducts function| relatedProducts object| widgetConfig boolean| tmLemurIsFirstOpen object| webpackChunk function| tmSlideModal function| tmGetSlideModal boolean| tmHornetSlideModalIsFirstOpen object| tmWidgetScripts object| __wph_integration object| wph_init object| _F_toggles object| osapi object| gadgets object| iframer object| __gapi_jstiming__ object| shindig function| ToolbarApi object| iframes function| IframeBase function| Iframe function| IframeProxy function| IframeWindow string| translation object| google_tag_data object| google_tag_manager object| gaGlobal boolean| __fd60252RwdConsentBridgeInstalled number| $smcInstall object| _adftrack object| _paq string| conversionCodeId string| eventName string| categoryEventName string| adqueryRetargetOrderID object| ptag_params object| InPostPayWidget object| __INPOST_PAY_WIDGET__ boolean| DoofinderStarted function| gtag function| a0_0x1758 function| generateQid function| a0_0x5434 function| makeRequest function| onYouTubeIframeAPIReady number| j object| INPOST_PAY_ANALYTICS function| preciso_piped_listeids function| filtre_preciso_categorie function| filtre_preciso_panier function| filtre_preciso_fincommande function| playlink_plus_product function| filtre_playlink_categorie function| filtre_playlink_panier function| filtre_playlink_fincommande function| jswebproduction_semicoloned_listeids function| filtre_jswebproduction_panier function| filtre_jswebproduction_fincommande function| __kwkpartnertag function| __kwkpartnertagcook object| AWIN function| AwinCustomEvent object| zx_products object| ccxtgSettings object| Piwik object| Matomo object| matomoAbTestingCampaignUrlParamList object| AnalyticsTracker function| piwik_log object| $smctResources object| $smctData function| addToCartStorefrontAPI function| addToCartLegacyAPI object| Adform object| KJUR object| adf function| hasOwnProperty object| usi_commons object| usi_cookies object| usi_dom object| usi_aff object| usi_app string| intentlyTabId boolean| $smctIsDebug object| $smcT5 function| $smcCallCustomScripts function| recovaOrderTracking string| nunamiSessionUuid function| nunamiOrderTracking boolean| nunami_popup_initialized object| lanternTracker object| lantern object| iframe object| _A4Atracker number| W2T_trackerID object| VeoTarg string| VeoUrl object| script string| $smcRecomminder string| $smcDynamicBasket string| action string| category string| product string| reference string| amount object| ads string| refer string| refer2 string| re boolean| KwkWanTtWcCdth75395_eyJ6b25lIjoicHJvZHVjdCIsInByb2R1Y3RJZCI6IjQxMiIsImNhdGVnb3J5SWQiOiJEb3BwZWxoZXJ6IHN5c3RlbSJ9 object| sddanJS function| docReady object| data_3987 object| s object| data_8879 object| t object| wewo object| apiEndpointURLs object| LB8879 function| AL8879 function| A8879 function| _0x9a39 function| _0x1a95 object| fp2_rtg string| cP_int string| prop boolean| rtg_ZmL0Zt== object| LB3987 function| AL3987 function| A3987 string| rtgUrl function| rtgSendData function| appendTag function| appendTrackingPixel object| uapnli object| g7HcBf number| b3V5si3 function| wrd9r20 function| DCt7_TL function| aNrX6j function| NEVAdVh function| K4H0AEA boolean| __sddanDataTag string| _1jmnnxm string| _1jgate object| _nwvdib string| shopf object| veoxa_if number| wait_nw function| Info function| getCookie function| uuidv4 object| beS6OIG object| zLSWSP number| IrqoBK function| ae0VNe function| lOdmb3 function| IQIXKph function| R4NBz7 function| aUZSHO object| webkitView boolean| _1jptlmv number| count

74 Cookies

Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.

Domain/Path Expires Name / Value
.wp.pl/ 1970-01-22
02:27:17
Name: statid
Value: 53df3e2c6c9971933f0b8c6acf715e73:3ac0da:1789541144:v3
.wp.pl/ 1970-01-22
02:41:41
Name: statidp
Value: 53df3e2c6c9971933f0b8c6acf715e73:3ac0da:1789541144:v3
.youtube.com/ 1970-01-21
21:24:53
Name: __Secure-YNID
Value: 21.YT=YCKHlMWw6-x1J4ZEh0WgjfvqLx0rTroeoeDaeTv1n-z1D31o1wYTtFqedtJeGjSr1t972Ice5Iv4VsatgbOfp4ABoLa7vah0zu0H4C_1etzZqNlOkwIzACwRzppqwbXr8x2XakUE2Ty9lfXgLbMxOl2KyfTyv9zxcusPhpN1zdKzgmIMhKWrIU7JU6Hsy-YKA0everUvuaONLQ8OE3gQHEYG59IB5lTfwwqR0t2MsRYQEakG0hpIcg48mhc5tRSisrXp5LuJ68xM8yrsbcGdTQJmLkdWTanlmpHYhAMUwwbBTr_uHBiA-GoD0B-KHHme_2xn_1-45-VXpKyLO1V1Bw
.youtube.com/ 1969-12-31
23:59:59
Name: YSC
Value: YQOcxjV8WTo
.youtube.com/ 1970-01-21
21:24:53
Name: __Secure-ROLLOUT_TOKEN
Value: CNyLgOy9ns6yFxCZr4KiwPKWAxiZr4KiwPKWAw%3D%3D
.youtube.com/ 1970-01-21
21:24:53
Name: VISITOR_INFO1_LIVE
Value: 08EdZ_lVSZ0
.youtube.com/ 1970-01-21
21:24:53
Name: VISITOR_PRIVACY_METADATA
Value: CgJQTBIiEh4SHAsMDg8QERITFBUWFxgZGhscHR4fICEiIyQlJicgHw%3D%3D
.inpost.pl/ 1970-01-21
17:05:42
Name: __cf_bm
Value: lUrIjBdtyVUa_PCVHLGrBQPDzrANuQJGcAcGrvQsDvY-1789541145.0419226-1.0.1.1-O4x7e1nIOsmm5Q51ofKZGQ.wiu9RBXVACOxhsQwrV_jifLZ_gUGSPWwB5zrXbMZBlUvxxzRoky1aCgBpu0nMqnkdEDsesitGQ3gFYaaVokd7uVsoWwchUvuyGYdF6tVc
.doppelherz.pl/ 1970-01-22
02:41:41
Name: initialTrafficSource
Value: utmcsr=(direct)|utmcmd=(none)|utmccn=(not set)
.doppelherz.pl/ 1969-12-31
23:59:59
Name: __utmzzses
Value: 1
.sklep.doppelherz.pl/ 1970-01-21
17:48:53
Name: AwinChannelCookie
Value: direct
.google.com/ 1970-01-21
21:29:12
Name: NID
Value: CokCCAESuwEBp2sxrn70SRuF9W8Wftd2z4gGvrm2gHFJE8ZU9qjmAFJTCC3gvu9qt-nwkuwv3PX_IJB_fkWmS3AiGmg-DWCUa8Q_ATX7GlKq3Wyx61InI74PvH8k3cZi31S-DQTMXPE4xT7ZaF3vABKdgZAEDsl5WKVkyWlkE1fWpXA_SSX1hLlI25Zx6WW00lRT-vSH4ijnQ385RAtfeyh0YOQZO_PYEVY4fuEQP_Z7h3A7M4UAZz79owi5HCojS1xbKAEyRQEOK94R4lcWz3A-bXraaupSG6TlOOreW07NUdYVEawZ33wufjEwHAXJEoLtk16DIRp_DBMGaQ-3Sv22LFGyfRWcxAp2Bg
sklep.doppelherz.pl/ 1969-12-31
23:59:59
Name: Shop5
Value: b8st7bmeks1ihvb7d7sddktjhp
.ssp.goadservices.com/ 1970-01-21
18:32:05
Name: statid
Value: 53df3e2c6c9971933f0b8c6acf715e73:3ac0da:1789541144:v3
.ssp.goadservices.com/ 1970-01-21
18:32:05
Name: gopluid-ssp
Value: go-01M2MFDQGB49HKTQP771PW8W3G
.casalemedia.com/ 1970-01-22
01:51:17
Name: CMID
Value: aqo7GlVbLbIAPFv1AIC8vQAA
.casalemedia.com/ 1970-01-21
19:15:17
Name: CMPS
Value: 3364
.casalemedia.com/ 1970-01-21
19:15:17
Name: CMPRO
Value: 3364
.smartadserver.com/ 1970-01-21
19:15:17
Name: pid
Value: 7837443725504992626
.smartadserver.com/ 1970-01-22
02:34:29
Name: TestIfCookieP
Value: ok
.smartadserver.com/ 1970-01-21
17:48:53
Name: csync
Value: 55:53df3e2c6c9971933f0b8c6acf715e73:3ac0da:1789541144:v3
.adform.net/ 1970-01-21
17:48:53
Name: C
Value: 1
sklep.doppelherz.pl/ 1970-01-22
02:31:36
Name: _pk_id.64.62f6
Value: c1832cfa1fe065ef.1789541147.
sklep.doppelherz.pl/ 1970-01-21
17:05:42
Name: _pk_ses.64.62f6
Value: 1
.doubleclick.net/ 1970-01-22
02:27:17
Name: IDE
Value: AHWqTUnw3dDnpvfxuG3nM8DsK6TLehZmL_FL1tAXoyMOz3SsLTLbFG9uNT9mBNjg10M
.doppelherz.pl/ 1969-12-31
23:59:59
Name: intently_sessionId
Value: b1d19cf42d2e9a3d
.sklep.doppelherz.pl/ 1970-01-21
17:48:53
Name: lantern
Value: ac2b78c0-fb19-4491-b036-f3202c32a7fb
.tangooserver.com/ 1970-01-21
18:32:05
Name: fingerprint
Value: ty%3D0%26cokdate%3D09%2F16%2F2026+06%3A45%3A46%26vsranka%3D0%26vsrankb%3D0%26userid%3Ddb38dd1e-ee82-4492-b393-6618cfe68807%26p%3D%5B%7B%22c%22%3A%22awi_dpp_pl%22%2C%22hh%22%3A3%2C%22H%22%3A3%2C%22L%22%3A3%2C%22pp%22%3A9%2C%22P%22%3A3%7D%5D%26isadblock%3D0%26icount%3D0%26icrank%3D1000%26rank%3D100%26ccount%3D0%26csrankb%3D0%26csranka%3D0
.tangooserver.com/ 1970-01-21
17:05:42
Name: __cf_bm
Value: UTVYAdbgzGL3tDxQ6r3VjLfCJdCSzyr9RsQ3kPwqWCI-1789541146.8443346-1.0.1.1-fac1Xt0GOgsPUoLXbpiOy8LPhXBkzQLu6gWbY4R4kjWyf2aLvtnBePelhSCX9QTLi6SP.xNQ4exOfWzQqadqYLGsXNPrD8ucBjjM0TRnvkqMwIzQ0oEUYqBXSoJp2oMS
.clickonometrics.pl/ 1969-12-31
23:59:59
Name: CCMSESSID
Value: 6fo0c7u7ql2mp2q237srnbiaqv
.clickonometrics.pl/ 1970-01-21
18:32:05
Name: ccxid
Value: a%3A2%3A%7Bi%3A0%3Bi%3A538210%3Bi%3A1%3Bs%3A6%3A%22373021%22%3B%7D
.clickonometrics.pl/ 1970-01-21
18:32:05
Name: ccx_uid
Value: 6aaa3b1ab68670fc980c2bfe
.clickonometrics.pl/ 1969-12-31
23:59:59
Name: SERVERID
Value: clx-app3|aqo7H|aqo7H
.sklep.doppelherz.pl/ 1970-01-21
17:48:53
Name: ServerAwinChannelCookie
Value: direct
.adform.net/ 1970-01-21
18:32:05
Name: uid
Value: 5351721985196806187
.adform.net/ 1970-01-21
17:07:07
Name: CM
Value: 1%7C1
.adform.net/ 1970-01-21
17:25:50
Name: CM14
Value: 1789627547_1789541147_1789541147_1_Hu7u4e4e4R4eAeAREREeEREREADg
.roeye.com/ 1970-01-21
21:27:45
Name: sklep.doppelherz.pl_lantern
Value: ac2b78c0-fb19-4491-b036-f3202c32a7fb
sklep.doppelherz.pl/ 1970-01-21
19:15:17
Name: vuidck
Value: a7cc3e0e-9704-4c40-909e-42a3fde0a8c0
.audrte.com/ 1970-01-21
17:27:17
Name: arcki2
Value: mu3qleer-xuTbhZOjQfifQaanToW2ag-ad!20210107!1789541147187!ip#79.127.186.227
.audrte.com/ 1970-01-21
17:27:17
Name: arcki2_adform
Value: 5351721985196806187!20210107!1789541147187
.rlcdn.com/ 1970-01-22
01:51:17
Name: rlas3
Value: QCZxQKpWaTAstDuBsN0zFE430iVjimIhFx6i+Det7iM=
.seadform.net/ 1970-01-21
18:32:05
Name: uid
Value: 5351721985196806187
.fwmrm.net/ 1970-01-21
21:24:53
Name: _uid
Value: uml27f2_7687217536871743710
.eyeota.net/ 1970-01-21
17:05:41
Name: SERVERID
Value: 20353~DM
.rlcdn.com/ 1970-01-21
18:32:05
Name: pxrc
Value: CJv2qNUGEgUI6AcQABIGCMLqARAA
.weborama.fr/ 1970-01-22
02:31:36
Name: AFFICHE_W
Value: Sr1pGQemRzBK36
.semasio.net/ 1970-01-22
01:51:17
Name: SEUNCY
Value: 7839589DB3F53B6E
.demdex.net/ 1970-01-21
21:24:53
Name: demdex
Value: 05182160400965987825571395172295940782
.w55c.net/ 1970-01-22
02:34:29
Name: wfivefivec
Value: F1ff0hWD1X6JoT5
.audrte.com/ 1970-01-21
17:27:17
Name: arcki2_ddp2
Value: mu3qleer-xuTbhZOjQfifQaanToW2ag-ad!20210107!1789541147375
.w55c.net/ 1970-01-21
17:48:53
Name: matchadform
Value: 5
.dpm.demdex.net/ 1970-01-21
21:24:53
Name: dpm
Value: 05182160400965987825571395172295940782
.preciso.net/ 1970-01-21
17:05:42
Name: __cf_bm
Value: er.KQxclNdsyOK.9Yhjy2r_60QXFaFLIyHnL2U198gg-1789541149.0778165-1.0.1.1-KXvX2OzneTiSqXJQ8oZfxJ25O4n26VVjPKKny0BE_IhwYzyFiNeqFMqTgL3vhEgOh3wremlZulgv1AKzbKpB8hBnADX5cYA80V4.Vnba9CQ46v26tuFwYX8pnO478Mlv
p.gsitrix.com/ 1970-01-22
02:41:41
Name: AnalyseUnique
Value: 365b940481879a53942c944f
rtg.wewomedia.com/ 1970-01-22
01:51:17
Name: uxid
Value: e7a67f4a-d47c-450b-a6dd-dbdb823de967:1789541149218
rtg.wewomedia.com/ 1970-01-21
17:15:45
Name: uxid-dec
Value: 1789541149218:B
.emailpartners.net/ 1970-01-22
01:51:17
Name: AP9FyaVf
Value: cktIeHNQTDNMWDZPcFFsSEVWcWgydmhLYzMxR1N1UHFiU1l4aXRaclVlcDFKZ2pVWTVIM2kxOHBScmxyOFJlNmkwY0IyZmJvZHBtclpiSEtwSW9DQisrSXhPdXBseURyZFhSY0J4czhVS2VsdmUvZEIxeDdpbEYwVE1QM0VDL2I%3D
.emailpartners.net/ 1969-12-31
23:59:59
Name: JzJ7A7rA
Value: Rjk0MFZ2cVhtNlAzVHJ1TFA0V083YzB4VXVibDVieGVkcXlVUTYzaGFnb2JtUzBPUzcwSys4SGQwRktsMElPSFg1TEVJSXZsSWJ4eCtNS0xtM3kzR2c9PQ%3D%3D
sklep.doppelherz.pl/ 1970-01-22
01:51:17
Name: _mc_uid
Value: c4b2gxg1789541149549
sklep.doppelherz.pl/ 1970-01-21
17:48:53
Name: user_id_t
Value: 5ba0f728-d021-4c4c-9734-365eb7e409d5
sklep.doppelherz.pl/ 1969-12-31
23:59:59
Name: ret_sess
Value: 1789541149555
sklep.doppelherz.pl/ 1970-01-21
17:07:07
Name: retuser_id_ct
Value: 1
ban.2trk.info/ 1970-01-21
17:05:42
Name: preciso_sid
Value: 99f2b388-0eef-4f85-b836-be9875bb3216
sklep.doppelherz.pl/ 1970-01-22
01:51:17
Name: adid
Value: 178954114967954
altopd.com/ 1970-01-22
01:51:17
Name: siid
Value: 37110409552
.2trk.info/ 1970-01-21
18:32:05
Name: dpp_pl_productnew_
Value: date%3D09%2F16%2F2026+06%3A45%3A49%26subid%3D_PROD%26sourceId%3D%26count%3D1%26priority%3D3%26destinationId%3D%26checkout%3D%26p_Ids%3D412
.2trk.info/ 1970-01-21
18:32:05
Name: fingerprint
Value: ty%3D0%26cokdate%3D09%2F16%2F2026+06%3A45%3A49%26vsranka%3D0%26vsrankb%3D0%26userid%3D77b7aea8-4f6f-4588-b422-79f02faff39e%26p%3D%5B%7B%22c%22%3A%22pne_dpp_pl%22%2C%22hh%22%3A3%2C%22H%22%3A3%2C%22L%22%3A3%2C%22pp%22%3A9%2C%22P%22%3A3%7D%5D%26isadblock%3D0%26icount%3D0%26icrank%3D1000%26rank%3D100%26ccount%3D0%26csrankb%3D0%26csranka%3D0
.2trk.info/ 1970-01-21
17:05:42
Name: __cf_bm
Value: H.GnayXuuqeZhmobEqx.H.Y5Nfxn_kWNrb8OCIMb2ms-1789541149.7071192-1.0.1.1-SsY8Z_5.cjp.tvZ4cNz.fmQgiXtPF1vlg3hhDuRWWYnaTx_aj5Z_.Aokt4v5HKOmSi86VY6dmCN8W9MOw3fcQqOtjWbtT2BZuglEZ25DFdXOo8YaiV2bn.QaAWWU3j91
d.audiencerun.com/ 1970-01-21
17:15:45
Name: AWSALBTGCORS
Value: rhkGcNmhla6E4ASpNBPc82n8TbHfY7y7NgFyWmNYNARb4k4nJU/6VxEWraY6spCUXUB30f4c5ii34bwAkDTmH8mphcM1Q4aBEbruzjTDnXCULneRRow2kOhqLWYhGQ4a9Yf2Hvt0ikgX1cQepSmichrr67cK6emz0DkkZeJMT4tC
d.audiencerun.com/ 1970-01-21
17:15:45
Name: AWSALBCORS
Value: TFZjdZzug66GaOvkZ3cpunHZtLhTPGE/QrqELdmceBCFB3CNjf4iDCp4sVO+WH1JpzKeoFCj3FpppVteWjeimK+56sq4NTKxagjCfCwbwm8xeHKm130UoxBJTtYy
apptracker.stream/ 1970-01-22
01:51:17
Name: ts
Value: cMpcAeA8lahZD4Cye0C4YMHRkaNfb6soa_2hZdt1_psmpxKVLG4sXXNC
apptracker.stream/ 1970-01-21
17:48:53
Name: rtg325000000980135
Value: wiwUqA94CfTIj-9nmnun7s8s3Qj4ov4egoZ-cmDHc-9vZM7CLSD6pABNW8DxPbzfjo5RSPZ_PHILoIKqToHdUXNBOPwBFxLWyX3WOQIxjgpEeT07N_pLCevcGSvxlQ
my.rtmark.net/ 1970-01-22
01:51:17
Name: ID
Value: 0883b381e03b449de149e5030c186247

22 Console Messages

A page may trigger messages to the console to be logged. These are often error messages about being unable to load a resource or execute a piece of JavaScript. Sometimes they also provide insight into the technology behind a website.

Source Level URL
Text
security error URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus(Line 50)
Message:
Refused to apply style from 'https://sklep.doppelherz.pl/upload/fonts/aestetico_regular.otf&display=swap' because its MIME type ('text/html') is not a supported stylesheet MIME type, and strict MIME checking is enabled.
security error URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus(Line 52)
Message:
Refused to apply style from 'https://sklep.doppelherz.pl/upload/fonts/aestetico_semibold.otf&display=swap' because its MIME type ('text/html') is not a supported stylesheet MIME type, and strict MIME checking is enabled.
javascript error URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Message:
Access to XMLHttpRequest at 'https://hotinfo.maxserver.pl/appHotbasket/script.php?shop=a96db86b9d7d6d7f128220325e99fe925c001520&m=1779714858' from origin 'https://sklep.doppelherz.pl' has been blocked by CORS policy: No 'Access-Control-Allow-Origin' header is present on the requested resource.
network error URL: https://hotinfo.maxserver.pl/appHotbasket/script.php?shop=a96db86b9d7d6d7f128220325e99fe925c001520&m=1779714858
Message:
Failed to load resource: net::ERR_FAILED
network error URL: https://sklep.doppelherz.pl/webapi/front/pl_PL/categories/138/products/PLN/?page=1&limit=9
Message:
Failed to load resource: the server responded with a status of 404 ()
javascript error URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Message:
Access to image at 'https://trustmate.io/images/widgets/badges/v2/pl/trusted.svg' from origin 'https://sklep.doppelherz.pl' has been blocked by CORS policy: No 'Access-Control-Allow-Origin' header is present on the requested resource.
network error URL: https://trustmate.io/images/widgets/badges/v2/pl/trusted.svg
Message:
Failed to load resource: net::ERR_FAILED
rendering warning URL: https://www.youtube.com/embed/RIenpVjeLR8?si=BHrZAFVtmPsydAwu
Message:
[]Automatic fallback to software WebGL has been deprecated. Please use the --enable-unsafe-swiftshader flag to opt in to lower security guarantees for trusted content.
javascript error URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Message:
Access to image at 'https://trustmate.io/images/widgets/badges/v2/pl/trusted.svg' from origin 'https://sklep.doppelherz.pl' has been blocked by CORS policy: No 'Access-Control-Allow-Origin' header is present on the requested resource.
network error URL: https://trustmate.io/images/widgets/badges/v2/pl/trusted.svg
Message:
Failed to load resource: net::ERR_FAILED
rendering warning URL: https://www.youtube.com/embed/RIenpVjeLR8?si=BHrZAFVtmPsydAwu
Message:
No available adapters.
javascript error URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Message:
Access to image at 'https://trustmate.io/images/widgets/badges/v2/pl/trusted.svg' from origin 'https://sklep.doppelherz.pl' has been blocked by CORS policy: No 'Access-Control-Allow-Origin' header is present on the requested resource.
network error URL: https://trustmate.io/images/widgets/badges/v2/pl/trusted.svg
Message:
Failed to load resource: net::ERR_FAILED
network error URL: https://sync.crwdcntrl.net/qmap?c=6466&tp=ADFM&tpid=5351721985196806187
Message:
Failed to load resource: the server responded with a status of 404 ()
network error URL: https://rev.owltrack.com/d/asyncjs.php
Message:
Failed to load resource: net::ERR_NAME_NOT_RESOLVED
rendering warning URL: about:srcdoc
Message:
[]Automatic fallback to software WebGL has been deprecated. Please use the --enable-unsafe-swiftshader flag to opt in to lower security guarantees for trusted content.
rendering warning URL: about:srcdoc
Message:
[]Automatic fallback to software WebGL has been deprecated. Please use the --enable-unsafe-swiftshader flag to opt in to lower security guarantees for trusted content.
rendering warning URL: https://sklep.doppelherz.pl/doppelherz-system-kollagen-11000-plus
Message:
[]Automatic fallback to software WebGL has been deprecated. Please use the --enable-unsafe-swiftshader flag to opt in to lower security guarantees for trusted content.

Security Headers

This page lists any security headers set by the main page. If you want to understand what these mean and how to use them, head on over to this page

Header Value
Strict-Transport-Security max-age=60; includeSubdomains
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Indicators

This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.

a.audrte.com
aa.agkn.com
ad.360yield.com
ad.yieldlab.net
ade.googlesyndication.com
afftrack.pro
ai.trk42.net
altopd.com
analytics.queisser.com
api.adquery.io
apis.google.com
apptracker.stream
ban.2trk.info
ban.tangooserver.com
bbd-tag.de
c1.adform.net
cdn.appstore.mamezi.pl
cdn.doofinder.com
cdn.logico3c.com
cdn.preciso.net
cdnjs.cloudflare.com
cm.adsafety.net
cm.g.doubleclick.net
cognito-identity.eu-west-1.amazonaws.com
cookie-matching.mediarithmics.com
d.audiencerun.com
dcsaascdn.net
delivery.clickonometrics.pl
dfd.doppelherz.pl
dpm.demdex.net
dsp.adfarm1.adition.com
dsum-sec.casalemedia.com
eb2.3lift.com
eu-u.openx.net
eu1-api.doofinder.com
eu1-config.doofinder.com
eu1-recommendations.doofinder.com
eu1-search.doofinder.com
firehose.eu-west-1.amazonaws.com
fonts.googleapis.com
fonts.gstatic.com
googleads.g.doubleclick.net
hotinfo.maxserver.pl
i.ytimg.com
id5-sync.com
idsync.rlcdn.com
ih.adscale.de
image2.pubmatic.com
inpostpay-widget-api.inpost.pl
inpostpay-widget-v2.inpost.pl
jnn-pa.googleapis.com
js.cookieless-data.com
js.smct.io
lantern.roeye.com
lantern.roeyecdn.com
loadm.exelator.com
loopwidget.com
match.adsrvr.org
match.contentexchange.me
mediaconvertly.com
mrtg.emailpartners.net
mxapp4.maxserver.pl
my.rtmark.net
o.gsitrix.com
octaadsmedia.com
onetag-sys.com
p.gsitrix.com
p.nunami.ai
pagead2.googlesyndication.com
papi.trustmate.io
pdw-adf.userreport.com
pixel.bsmartdata.com
pixel.onaudience.com
pixel.wp.pl
pm.w55c.net
pprzesylka.maxsote.pl
profiling.veoxa.com
ps.eyeota.net
rd.afftrack.pro
redirect.frontend.weborama.fr
region1.google-analytics.com
rev.owltrack.com
rtb-csync.smartadserver.com
rtg.wewomedia.com
s.ad.smaato.net
s.retargeted.co
s2.adform.net
secure.adnxs.com
server.seadform.net
simage2.pubmatic.com
sites.adquery.io
sklep.doppelherz.pl
sklep685892.shoparena.pl
smct.co
ssl.ceneo.pl
ssp.goadservices.com
ssp.wp.pl
static-cdn.trackier.com
static.doubleclick.net
static.inpost.pl
std.wpcdn.pl
sv.ciblelink.com
sync.clickonometrics.pl
sync.crwdcntrl.net
sync.teads.tv
t.nunami.ai
t1.adquery.io
tag.facemyads.co
tagmanager.sklep.doppelherz.pl
tags.fulllab.com.br
token.rubiconproject.com
track.adform.net
trk.retagtraffic.com
trustmate.io
uipglob.semasio.net
user-sync.fwmrm.net
vu.adschoom.com
www.dwin1.com
www.google.com
www.googletagmanager.com
www.gstatic.com
www.mainadv.com
www.upsellit.com
www.youtube.com
x.bidswitch.net
ban.2trk.info
ban.tangooserver.com
hotinfo.maxserver.pl
match.contentexchange.me
rev.owltrack.com
secure.adnxs.com
sklep.doppelherz.pl
ssp.wp.pl
tags.fulllab.com.br
trustmate.io
103.231.98.109
104.17.24.14
104.18.0.2
104.18.2.89
104.18.27.193
104.18.31.101
104.18.41.22
104.18.41.61
104.21.10.19
104.26.0.138
104.26.10.75
135.125.170.28
142.132.237.132
142.251.110.119
142.251.110.154
142.251.14.101
142.251.14.113
142.251.14.156
142.251.14.95
142.251.156.4
142.251.157.119
142.251.20.148
142.251.20.156
146.59.84.109
15.197.193.217
151.101.66.132
172.217.116.4
172.64.146.195
172.66.166.111
172.67.150.171
172.67.159.95
18.134.84.75
18.157.227.77
18.197.44.30
18.198.138.71
18.200.137.183
185.31.26.219
185.41.68.192
185.41.71.25
188.114.96.3
188.114.97.3
192.178.183.157
192.178.183.94
192.178.183.97
193.135.9.133
195.181.175.40
212.129.3.113
212.77.113.26
212.77.113.48
212.77.98.32
216.239.32.36
216.239.36.21
3.120.74.76
3.131.73.36
3.174.46.3
34.102.136.131
34.102.157.203
34.117.39.58
34.149.104.117
34.159.90.131
34.241.233.208
34.242.143.121
34.249.139.175
34.254.69.83
35.167.241.13
35.210.130.15
35.214.136.108
35.214.217.206
35.242.250.78
35.244.159.8
35.244.174.68
37.157.2.13
37.157.4.21
37.157.4.29
37.157.6.246
37.27.169.254
46.105.34.150
46.137.100.189
49.12.245.74
51.210.24.88
51.38.158.176
51.77.41.26
52.19.173.53
52.213.207.85
54.171.79.239
54.192.35.44
54.192.35.76
54.195.115.7
54.36.150.186
63.183.69.9
65.8.131.85
69.173.144.138
77.243.51.121
77.79.221.139
77.79.221.168
78.46.234.191
79.137.99.232
81.17.55.173
82.223.103.149
85.114.159.93
85.195.73.74
85.195.93.95
88.221.170.40
91.134.222.90
91.134.222.93
91.216.195.30
91.216.25.161
92.113.16.12
95.131.136.1
99.80.34.227
99.84.152.34
99.84.152.66
01d5a4b445e0523715bc8f1062e7efdc2473b2d09b084a70f4c1d9676d52515e
05b557d5989e0977ad7d6bee47698a1b0582a6dbe6b7e2e1ebb04fb95b54ea2d
06778826e14e51d6211800d4fa8b7a6db32a58d0a05f72acd87a2bbab0b9328d
0715f063788e713bb8f23239537c1c5c3b5c8ecdc5a28d789dc6ef35a25079ca
0725643f343602db374cfdfec1b6d124e88964d21bd6efb7b20104c49e8358c1
0ae4bfde2ffb91cb09d871fb260ff96c8c399dbb68e7e6320387ebe57fb17189
0b2451b6ceeca58ad8838ad068a174288107ac1895b597ef13cc3e477ef38a52
0b8a20373c6dd04e091902226d922b3688143a8938afb9d283d889de7b55ceb5
0c491ed20fae0cf6d082339fd5758800109ac0dd8c17667c49543d42363097f7
0dd33d7fb1b6511c13d0b43c3459f6735a1fac78e6de60aed669bdcfc9f491b3
0ec1b2f1d5d75d1c7cbd1af2a58148327d1cd75ca49316ebfb1a1857bc7786d1
0fd28fece9ebd606b8b071460ebd3fc2ed7bc7a66ef91c8834f11dfacab4a849
11a994ac5e338efe9b356fca1cd765e2d946bfab26b8d66c649853d15b8eff4d
12047d9cec7d2c20a364117e5952575290afe090049eff831358cae1e4d2a909
1382786d10045c02d2ba5d7a2569045b6fd5f41fd6c2db17325897646b78473d
14e5b2f4cd21cdeabde3b642066afda4d92b8347b9d78c64d414bb3cec5bc2e4
150c271bc18110a455847c8a1a9977d49c500e5303bc63ed79af11ef688ad1c6
15bbb20f775d60e73623cbeeb80f97f40d92466d7df84fd517b388e09675e73c
15bcee52d985b176245cc0c630167f32dc498053691861a61deef863c69741d8
16bdb2bc2952515ea9f7034108cc922c9b3e5ffa72d643e1551e241edd9cb744
1708f9f0aaeda02b7e0645120d4d17e7e92cbc07c94b648d3c0a250bc61bbad6
19ec38dda2432d729e75c2c02c3b3ef83aae74029871cdf496d58f0c1b2a942d
1b366d882f8320890ed6d040705b9dcff4cbfa1b0422d9c1972e54bccaa395c8
1dd6cdb6928c518a0e5e8471f5efba8c8ad2d4219cb9fc1e113845ace1f51ace
1e6f131e5c23998532caa01dec741cd746efdb7364cffaf33a43f227aaa0d458
20409ae125229780e644e1ca29cfecfdbf283b9e495e343866671222f29d3b83
20b535fa80c8189e3b87d1803038389960203a886d502bc2ef1857affc2f38d2
21d0ac00a9c583ac821b385bf13653b0156565ba2002ed07f00513469ecf78a4
2279d34a095ca33040f7f9d86c7de1ff7d2c14a4fdf7f9346c77fa8f2f0d721f
22822441dbab76d710c8b365045f60825c313ccdbd94c3d5e744b29d64004b99
22f4aadb4161427bd826844d8682e474361a17c13a15271b44b68a1ec62324db
236c948683a9914019dd81d7b331e9bd4e90b0adfc8c5d49687e6e086f6aac35
2452fedbe55b2a8160ccc7c7490ade42ec4b138fa01054f37b8c160d10892328
252d53b28c2f7a0547c23876dc56846abe13d6a5081a50a347fd265a7d42d383
271facec764173c55dbefc01f507d328fe2bde80ca9aa1b909641828dcdc599b
27e40039731c83667839dd239bbe6f1f6108925bd8cb9aafd6794cd46903f11c
282e4d6eaed8b34d6cf4e48e09433dfe98d41cd02a4dbe4111e5c64859ecf76a
28d0dbe614e89adcb3cf3b7df6b6408eb862c831239813107b3493b8b952e78e
28f653cd85eb808ad006e0e5674c09bd269984e6d1fdf4de7e93fbd8caee1894
2aa4fa20701cdd6d8d56046069001186b5267e3ee7d0ef618ad2f4a683723e11
2aecce5f3002d9b52dda7dee72c341653d072a7d8af22121bf518532ac542249
2c20e3c8e25f086d2876ad6c1640989c834448f299d2e72e4346a32f67258d1f
2dba359a3996c17197c837187e64008c5f28ce57708a56682425d94e8545a76a
2ddeade3a8991666b89f2a0c3aaba4508852838488781e260d45bc886f1172a5
2e0ebf9634e3de6550e1c41af6b81954ac148c2f54f821a2b1fb138ead8333c0
2e2fff74ced6664bcf4e19a8dd4351121e7b1fb3a8f892434cb139351cf7c829
2ee21c7d7831b20eb9727825a46c2b7e609b14afb1531a6ee36921e31a62ccfb
2f561b02a49376e3679acd5975e3790abdff09ecbadfa1e1858c7ba26e3ffcef
3100e775e8616cd2611beecfa23a4263d7037586789b43f035236a2e6fbd4c62
31010610920112383dbc36f5afadd6a3b5be355f7046e8f64e98f1b154a8ce07
3171af41292a0a68db5f7f26c3580465be72e5e6a0bb3cfdcbdc54254536454b
328e90a318268aea96180cc31666ae6d6f79d90d078c123bc3d98ee08a192fb7
34b9c504cab7a73e37b746343a449132e56cf7b5481af2cb81dc74dcff25c956
34e8f312f56bdb728fc36d417d6b713c54858713e32bb12a69063ca19d15210c
36031302e14a6d87552e7dbdb754bf3e977e211e867185b8159f9f15ec5ad235
3a2d459adec3d78b95511ee25423235aabf6ecf35b24bed5605ec5ecb7c1de29
3a78587186ec7377a4706df9236b46dde257c3a17f0856b19c59d16e6ded76ea
3a91a95c37ebab405756cd9475169f4483af9a5dea8a3941a2915d7c363eeecb
3b7b8a4b411ddf8db9bacc2f3aabf406f8e4c0c087829b336ca331c40adfdff1
3c33d32ca3c3a71694b27939fb34e90de917438b11bc4b339d0698d904dab910
3ca724904d4393807243f6f6aff87f2c6652de1486708a02e42b1a7e86d2d7d2
3d15410482ba2dce1cd463f73e97396affe54bfde9f3a61dc89a8af1c993eac4
3ed35cf9ad778c757574790425fbb79599fddf51120beae4b862fd847c18946f
4062edaf750fb8074e7e83e0c9028c94e32468a8b6f1614774328ef045150f93
4067f5146e4ae5178fcfd00cae33f20b160da24dbc611ddc2d880b82f8c439f7
41a7e41ed792f06f2dcbe5335494d5180251f4050d9420de8e33fa83a17e8311
42826ef0ceac082157fa0cda61701c1ee2a77719e550a47c7d3bf504cf7c8b4f
429413266afc579577d4d13a90a9eb3e29a9637b74c49ed3d6ecc0e6e861edd5
431179aaa06d94305ca7d88cd4437536c91cc8de41e1e1052b222a8fd4e5aa62
43ad90cbb5676957399f2ad5d477d3e480505594ebfe061ab34c84eb55d43d13
45336bf2c27960347588ebaedc466e533d74cb661ed98b7d8b45c27a54e0e596
46093e6d7d2d64f56fade236b081136d4dec25a7ef591576e20183a8238c981f
478671d055c158d48c18d24c014fcdc07dabb5ee810c929484774b14315645a2
48062ea02ec57d525aaedca180131ae76c4f2ad6fbb6153a37799533daea8a35
4862a07078b7462e5d85a0a2ab5b49bc3667036e10fe2fbc04c4da9b7b3f8cfb
48914f8d390cea31360e88a9fe8af32fa81f1e81dee479838247d253333f2df9
494308d422e33784eaa98d5027d01e9774b731928114817a632688e890e3e287
49c1cee0872913c07429752eb0a6c8304cda60c775ad28c47005114754dbbc2d
4dda8415527f60f66f42c7b9e07277e97b142c3c3b52d553cbb2490fcbfb99a8
4e0705327480ad2323cb03d9c450ffcae4a98bf3a5382fa0c7882145ed620e49
4f5de075438bd75327e313f024cadadef487c7864a364eebed4c5940bc3b0d55
4f8006ce48b56bdab84857e288b79f980d6c3243909010760b231005a367322e
517a673d22e83eacdb62bef3b37e4d957e6ecd73ba590426da1656213560ec30
532dcb7076bdf1d2b249d0266673a1f4913c68b6efaebd5c7d88ac587b33fd0b
5351e5f1d2ee39e720c2b16dc59b3d241373085a281f891cd93da9596789418b
538fb816c4684719da4b865541678b8989a21b87509951b3e0605a943e5b28db
548f2d6f4d0d820c6c5ffbeffcbd7f0e73193e2932eefe542accc84762deec87
556fc0fbb171c81ae43b5cffa207a33d18636c7fce9da6b347749f5650007c8b
55f37deb8b81275f66bfbb386c9700f74b06dca4111c5a1dc457770d86bf49a7
56eb6089ee43b1f765a9919693423813fcf856a6068933064c72f5529fd51e54
57a0d0328187c357c348e41654bd8afd77fda3dfccf9563dcfef61a297babf4e
58180e3cba5a736e1875c690b3a756dabc7ee19960f4c66a692d42e5679c13d0
58687cf19f5c4523eb3937b05cb26fb6393d533151ddeea203cdf4c37fadc043
59938868870ce60b8576506d0211346d8a85329a9d54997c39d921389c493b34
5b3334e5d1012f83b1bb44a6d63c132bb908c334bcf8fb8c0800df739eb52c33
5b6ebbdbf28460356b7d1639418aceac2946652eed37a423f1465943658d3182
5b8f987f90f9a084e87e153fd4be8d037362202681f2b17f5bbc0cc60b811541
5bad2c32517cf14baa185e75a0f27d25b9d1dfa75317cc739be7177d444a8b81
5e439f78662b66e168243577f73e81eb3a5c7227d2b530142f666d2e3fc2cf9b
5ea63270f0913583a9b5763305d3b971bacf709d8640055654de563e2286b736
5f79436bc01391d1fca66a02f7fc3e3a49cb72e3e542932df985b30a3d706c67
5fcac030d205e29a1f983dff90e05178f8daf61e948c3abdc1dd862d09765b99
625a20fcf54d921900a762961a2ddcefe135ee540a5b95b758fc2dc5eb3bc375
62beacb54fec9c638996da47114fd52e101c451cac6a7ce6dd6b66b410ce7fe1
69015d24758dd9d4dbd955d98f36d49e4aa6ee18980fa67fd89f9f60760edf97
69a94e631a810ca34a04492e865f1088b16a1863bddd838f12de9e85844485d1
6a842ea462daca2a0b5a0f5f25bcfc8e0059ac811ca6c6a1bc54e4d9119621c3
6adc3d4c1056996e4e8b765a62604c78b1f867cceb3b15d0b9bedb7c4857f992
6c357c6789e3c945e2e6e88ae3eb1b641c90bb8ab45c1c1b18c112aff6cbcf04
6c71dcdb721f35868d78d7a81340ba039e36fa599f2edd83154b5ff232f69dd8
6cbd3b98bf49873d5137daa50e8074a5b3071ff63e8915a8b34174c4d9feb96e
6d3583a3f5dbc4ce59ea437e238a52ce5e8c9c948f64176233d92b3a772eea3a
71ac195d6650b7750eebb43459d0ee876634248bcab13c495ca7d35c712856aa
72431f67caf662916d7e087014a84fc06db938d5ba9abda94c92a2532c7ba125
727eb2f382eb0c30f6b759072b16185eaec93666000960f7fbc5a384f66c4b1e
72ce74fd5abad46c8c353096014aeb21c25f66bfb03ec1ffbfc91803fa3702c3
7829b459cbc4217a45db28e945b2e452e461d0907a09eb4414cd633f3c8444cd
78a7a3c1c34559fd5864aba01e7a1f20d6f881259c8b32e28cfa9d6b2801f35f
78fef654fe4087e4f21039ddda38ad941c5b7ca86e557ccf7e390852f0dcd0d6
79de2ef4fdda9dbb87fe609306bf5d6b3599f538c1202f8e06500eec9f70c002
7b0e1348f28fb277b049d55cf086b1e7baf7cc06d9de37c6c7ae2941fc759acc
7b67b770e711d5e0978a15d1cbc18c38b5a2fe524383b3d74017da080937e327
7ba6c4ff950c37c27dcd1a63f7b1b2620baa13048db47f23caaccaf02245ce08
7cceaf0ca77192d6425528a063348b48a76e41428822f9db1d88e5370f05e6f1
7ce358e16e04aa985cc46d7fe62cc3258ac925db741c20e32156a7909a9acf27
7e8d91e33c298ffdaf81c29a4deb12ee1a0ff1ea5947785ac385ed0b0337c17d
81cf3e24863d159b577250f05e92374755f0984c0d0ec88b8bf02c080f65dcaa
823b0d21e4f3045ae381c91e418036c91449acbd965333ef1dedeb96011dc021
824e85572e5cf8dee8943f85e6938b69b2ddd5bc34b807b12dd503ae9ac23532
825610ec409015e347107df643e38e29ea1b7f7fb02bd61b8f1a1f8463859049
8337212354871836e6763a41e615916c89bac5b3f1f0adf60ba43c7c806e1015
8855aa7442ff8bc3e1cbc3b394ea694c8211c4ffbba83c699fc27fdbd6cfd734
8857e1c0419304f0dc9cb82d125512071ed0f44fd4e5b00e228f67fcfb9f1c2e
88b00559cb3ece9b794d19591ddaa16fca0668d4d41e4707f1b4d1c92f326124
89aa9f3b9b9ed156d219c122427f8e797c67c4030adbe4201d72030396d6b462
89fe0ee6020314794fc2cfeacf3d10c31050cfe56f8ebddf1ed0a33fbe941fa7
8acc1e9aed8df67ce763aae3c9d9ff6f6b963eacab2009c17c0395f88b5aea1e
8c3e9e92573cc1a85c0b47b9d062cd2a33cf60f2b46aacf1cf6ac7d36472ccc3
8d1923ba5c9d3c5c95a94e0fec5d32b7fea8b0e2e48e6491a6b5c054ebec067b
8d70b3e6badb6973663b398d297bb32eaedd08826a1af98d0a1cfce5324ffce0
8e1eb079ac3c2159726f68156036203499a9b4338796a5c848a2da72bf910df2
8f704806dbedeaaeca334b11ec348bc3ac3a439d6431544b3afb54f534ee4967
913512af2ec36b2c6b44baa5d5645e05f218c22cbad303fcbdf4fb162427db99
93ae7d494fad0fb30cbf3ae746a39c4bc7a0f8bbf87fbb587a3f3c01f3c5ce20
96fb40d39a9c00eb427de8106327259fd0369343343f54210a224094f8806107
97fd6fc793cd02667ee46858c161ecdd83e9f530673cf4de696486fb14087b59
9867a72e13d80f844b2565b31866531b240bba7afec45469b1edf3f808a4d874
988608fac85569df9820a19648f260d4da4514e20de84e886adcad97d8aca7c7
98f207904c9d527560c3187478b53ace6c1b59f88c2dce829cf04f963377646a
99c2917ee5b2a01459a923bdd1c676f15ee73b62b87f696e6735312d26f51e12
9b3827f630e8e34b75102a116bd386178ac1733537367f565f2525357dfd7630
9f071f1ca8abaeac147a749be1063dd6b1b5b1a2e7f1d45bae67ad94e36ce16e
a065920df8cc4016d67c3a464be90099c9d28ffe7c9e6ee3a18f257efc58cbd7
a0dbfa59c26550e7190a8dc17ec33fbab2de118039e568c4fb323b197f30b34d
a31e763cbf129bcc0ad0582eef3b22dee0d82dd80fb0555934f2ae8a1a64a145
a35e321c618cdfcf0ccef374f79e067954985aeb624d4b76f301870dfaab41e0
a3eab44faae5ebfa71bb638c643fff0c6db138c2125fdc8bea8cac41039636aa
a5a57a823d4e1d8048e9d9d3f837b3d21ee92b66121727853ead79b16d5542b8
a712778c4c78b733915ae9486bf678c2e34fd7f4038262548adbc5680ea13067
a88edde0efac58f74191dd77dd33b4e72416c28e686c2bcaa6683959a7e15df1
a8b7c779dec08a89faec495f6c654f263edc35b4fa24f22fe2dc9e1de722a6b2
a9e70abcb6b8e33b7b6b47e3e48ef70d4766af7ac8d473d90840880203d1ac0d
aa03dc59bdca72631d2301e4297cfa030bd31b907dc138e7b973d12311c90a22
aac07ec04684c78e426aeff7bb5fbba1a807abe0293a679f6c47ec3d0e66a4a2
ab55a1d7e38664843675f1677ae228cd33d8a1224438f1050f8a55a0245dadb1
acbdf40736c00c1aa4259b69eb015a432f539637cb63f4e4b6a407ddcdf4cf3f
ad586be2e7f1e25d36fb1bc35e102a0d2a9701807aa3f29815ce5e46f0681949
add143c285a6823f0ee462bdb906d94912ea79747fb872d1c7779d76a9f36032
ae4a852f56445524c99085f0bca7ef0cab6c6f0a31b4ade0b1393fecf0c778c3
af6057f5b86a3ea981b5c84c060ea7c9daef71c9084038a47eb3bbd807f5831b
b1442e85b03bdcaf66dc58c7abb98745dd2687d86350be9a298a1d9382ac849b
b1c44063e9e3fd49af401ac0bc76dbb9c5b059018d43d1e29709e72f3a8a2a6f
b1e3a326b58cd12e602331835447ca917f15158de3d667dbd234cca3ece8e546
b2e9c4b1b79bcb2769410bc28f0a690d1cb508d20b3acb46bb4c0657ce62392c
b4c61947bb1a0bf46137576db451d1893e11058d98f591c676d96be5b4d1276d
b4d25cac33d1ffae5d09263f4f7b9444061131ce78dc652a989366812b4de2a1
b5c0bc721b9625d08a45be005e83ef7143e3b8640afef96a3283f53d2f3bec82
b61a97a082469e51d111f4e8e0f7e1e8d7dca01dec46d3ad190095ed440e7bd3
b6a9967e221c29d5fe6122c114ca519aa3899b47e72fe9e0a2f4e0b35dff4883
b70fd1f6f3b7cfa655772cc3a20eb9e74e85d5f2c7f6d9ce2cd645e9f39ab82a
b93064d21480c5124df876c3c8e61a022f0ef7426c261ba22ec3a0d1fb09365c
bb1bdfe0673229d24b730ae82e0897a629997352aa790cbe71194d9e578b3480
bb229a48bee31f5d54ca12dc9bd960c63a671f0d4be86a054c1d324a44499d96
bd416788a3100151508a9baeb237a9484f7ced0a583a6896836a14c4bbd3057a
bdccf500c0b0c6bbee6a615f19941c79181ab729da53fdd598bc8aee485015d4
bfca7a4c18c0be53ab27977eb50f79e6f7d6139eb15972ec2cc8963852de9ec0
c23d306bfb0f833c5d7c58720d44bbdb2edf785ab31d7ddf709628b0ed1e60d9
c2b392d5064f8111106e1a1034d0b716b946a8bc0d9a7811c3209502f0a5d272
c3d856cc20c7b6a77ee63d0577f3ad804126fe8b58999496781e8b94cc4ca335
c44657b7380949b4297c7a1408865de5e73547c9f63c4cab1fa061942dbc7ac8
c9c3d8b7bddb02e9da5196a4568ee666123b9db82764e6e76bd74781a456949b
cb3f2fd3ae3327535a435ad6416fb4dad5192fa841384e370d32d03b2b40ff19
cbb7c5859592f52cc19c7d9aa0ee7e445d30f8797230915f5ef449ba3799c36e
cbcebbe83e989f5a35dd57e80810bb826b665b4a4006025c5a2675c2cc08b952
ccab4f569710043cb41590788256e2da858d4939f872352a902b8d0a90533d17
cdcd4c0c0f00316e1f630b442a2f23c465bcf83639fe790841abd8a0098e6216
cee6bfcde9890d4b56c653d637bc81ac31dd7007a96bf60e610bc900202c36fc
cf4724b2f736ed1a0ae6bc28f1ead963d9cd2c1fd87b6ef32e7799fc1c5c8bda
d0a7fe248eb05e77c77dfd4cdfb32e6ab9ce59458f1e8716fc1dec4c080963de
d1960e3210bb571e5a0f2d01c2f0c9be536122a4f886c21e78db67713cbba246
d291f83b76832e96aacd958217ede0f2309904c18366e326b2e20d9588a3ae3e
d31bc11f551e8d8ca03647fe969ea1e7bb0ec2aa429cb85a4a49935d24ef4b73
d3c033fb8fd265a34e85eeb41df0a73a6ec7865a32ba3be75ec98baedc97a58a
d3fe90218f83b6f548244d85b0be20ae170b15802a61a3eb193596c0b2d4c748
d59bed3d53c4e63f3358774eb4537017ad90da5a4fcbae205dd8880fa625a65e
d5c591af27dba359f1fb822e5d0b1e23750fff8a86ea55e7b30c950fbd35a6ca
d5c9a3a2c47304fe98c43aa058e13eedb8202b7e317bc56f32dbda493bab2c5c
d653f70eae4794386d3171660113acfa6bf1a78e32fb26c53ffca6b1701537dc
d7d5e54ad1e33d7ab49c664323ced79cb9723ff15e9764cd0edc3e15208e8336
d7f8473a05febc55f00d282ee211a745afe54dda9732fb11b4d1e8e6f3a3adf5
da1d86d98f124bff30527f5e86ba5f770d21a9dd30c71231f52ef5afaaddcbaa
db21f6b5d4f3d1ff9270df084c6e8fcbcb7fffa401ab603eb39f1270676b3a84
dbf653f04084c779b785ea88cd2792e5436a3bd320d0e7588545412233103c01
dce698380cf451415db4698d5005ae4f287cbbcf70771e19e4997b4ad7663367
dd17587ea74f09a0b739c47f2483899bb38f983bd3f59248a8d825d84ed3a2ff
ddf6e17bb70a67b80c1a6f4bba1f53ac7373589e3387aa416b957b573398979e
de3a7b45086f9561b2d67cf89d988225bac9d1a005b3a28112b342342d011b0e
de7206e6b64cbebf681f979f3b134a27a5e0c00f2c3bd1f1f4ad4e500ee97685
e0934767b60d322ba7e49ac74ad92ae10da86c0f775b0cbe412fffe27950e2f3
e281dc1a34a238f2ca5e06db4f30a77c173094ed34e4a4bb564d66c100291883
e348cbb735743ddd15c80f083a37f27c65d27d89431617db8021eeb518c78a1d
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
e42a5930d9cacbe10862c1f2220e2af95ecbb90abce186ac4797459e3e7cde78
e4e78ee1d2abc8e8d66e574c5a16d1e12e76c4b7a12df0e19435f39300afef48
e64954dc34e12c7190cc2338a54b07644ff0f102aa71cc7209bcbb49c3009f7c
e77ddf6d872e25c6859182b24337ab033d70f34756d5d636c8bd6e8531a6be4d
e8eabe5ddd83aef657b33998b8b65b469b11cff6cffe0c2e5b18cb1746f071bd
eb1f13a3c5a2db58c3fcf46fb91add8f92fc0687609ee0cb5c5b21f814efe365
eb2298c95a2861580ba717af6124123498f81414b6830952fca9d7d5b6bdaf97
eb47a6bcd058832111e35209b3dbd1900afc44ac854f7588f2d9927e1757a54d
eb94852847a67a9bbb35b69beb319ed42f3a5e2d4ab53f21db2ed623d5159c86
ec1bedf7dcfd4410762c2f576adc210ccadcaa8ca082553bf767e6ad008aba97
ec7b5fad608d36d16f65939bd09e70b4bb81446fa7ee32b345d0c2e4fcd174b7
ec89ee519f3e35a1651bd4081b04502e06f2bf11f6c80122a1cf76c60eab2425
ed31b8cee3cce1b2d13f51ad332d9f8a9264cc415832fa8be45f285caa76a26d
ed35be425b5c4bdb023df25d8c785e27c94e7284c6c0696074b57b7445bad56a
eeb02e62df4875965ff9c2bcd9ba29e6139289375059e9fc714cf5ab90ae6837
eed0dc1fdb5d97ed188ae16fd5e1024a5bb744af47340346be2146300a6c54b9
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
efe1fffde0e6048ed59531c1ef360bc6970620d39e97db8d6b20cbd252c669f8
effd4299323311672d4b36d1cf9e80442531d96c440f9a2bd7c0294dbb34a458
f29f2543444ecbde565c75bd2f78228b7b2a4adfd0cfbadbd776c4221e32aae3
f3ca3118d9eceb4028fb8b62693e34913badaedfc8d62eed83ed744697bf12f9
f576b04fe1c63a962302864e0237b8fac7304d84ec1eb640a7accca76071c7d9
f5cec2af9e0ef8787173dd1c3dac4170d377aedc63c353e1f51299fd1356a050
f5ddabb36e171a9a75696b7260b944c7c5af36f6389ef66e2a25e9422ca6b42e
f70f98cd38ad7a9e9faaa25cfbd4bdb9be1a622bfb3f2edb8cc4519d7c286f9d
f853b689da6f6a36846e73f5c036f7c8e322404e4876746608b5d9766a5ff58e
f99a2313e266466791ecfd25934d97b1364fbac993822367d46ffeb0fae2263b
f9e0c59e68d5550933488cf67f58f44f0cb5d2a3dd1baabfcf755c46e1d699ed
faed7153394c929d9d0faec4ed26f1796b72f819858c48dbbd916e4b16d149e7
fb968113803313a2acc4da23a43819bfde29ca9d6d2f4964d4a15d55eb0d276b
fc6fe0e4ae32f0bc3654f2151b99224b763545e4ab6ff020e0c18d250c21c4c2
fcd1e5bf7576c1520e9805247e923cd6efd2d346376b20f94dd07f445b82fc4c
fd988db891a09dcd2b69471bf1195994a2bf966e9c4f716e5fdd49b9ae8398cd
fdc0cf5659fef3148d9f8a0f94e7c0f35d1956cf4b212b2ca85c07d2542d596c
fe1b2a1d70d5d2c68da5b77054bde21b2e9925bb7b682857abc5bdc1d44a8bbf
ff4f17d21930e36d6d93baba663e624cb767afc3feebf7adaebd82242638de05