
www.pukacreations.com
172.67.212.177
Public Scan
Open in
urlscan Pro
http://pukacreations.com/ 14yr old
Effective URL:
https://www.pukacreations.com/ 14yr old
Submission: On September 30 via api (September 30th 2026, 7:55:15 pm UTC) from US — Scanned from SE Go Pro
Only in urlscan Pro
- Select different country locations for Private Scans.
- Use a global network of additional scanning locations and residential IPs for scanning.
- Interact with pages while you are scanning them.
- Download files from remote websites.
- Scan websites on the Tor Network.
Summary
TLS certificate: Issued by WE1 on September 8th 2026. Valid for: 3mo.
This is the only time www.pukacreations.com was scanned on urlscan.io!
urlscan.io Verdict: No classification
Domain & IP information
| IP Address | AS Autonomous System | ||
|---|---|---|---|
| 2 56 | 172.67.212.177 172.67.212.177 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 2 | 104.17.207.5 104.17.207.5 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 7 | 104.17.25.14 104.17.25.14 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 104.18.40.68 104.18.40.68 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 142.251.14.95 142.251.14.95 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 2 | 104.18.1.22 104.18.1.22 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 67 | 7 |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| pukacreations.com 14yr old | |
| www.pukacreations.com 14yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| cdn.jsdelivr.net 14yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| cdnjs.cloudflare.com 14yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| kit.fontawesome.com 7yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: pm-in-f95.1e100.net
| ajax.googleapis.com 10yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| unpkg.com 11yr old |
| Apex Domain Subdomains |
Transfer | |
|---|---|---|
| 56 |
pukacreations.com
2 redirects
pukacreations.com 14yr old www.pukacreations.com 14yr old |
1 MB |
| 7 |
cloudflare.com
cdnjs.cloudflare.com — Cisco Umbrella Rank: 284 14yr old |
106 KB |
| 2 |
unpkg.com
1 redirects
unpkg.com — Cisco Umbrella Rank: 788 11yr old |
1 KB |
| 2 |
jsdelivr.net
cdn.jsdelivr.net — Cisco Umbrella Rank: 280 14yr old |
41 KB |
| 1 |
googleapis.com
ajax.googleapis.com — Cisco Umbrella Rank: 617 10yr old |
30 KB |
| 1 |
fontawesome.com
kit.fontawesome.com — Cisco Umbrella Rank: 2491 7yr old |
|
| 0 |
jquery.app
Failed
cdn.jquery.app Failed 2yr old |
|
| 67 | 7 |
| Domain | Requested by | |
|---|---|---|
| 55 | www.pukacreations.com |
1 redirects
www.pukacreations.com
ajax.googleapis.com |
| 7 | cdnjs.cloudflare.com |
www.pukacreations.com
cdnjs.cloudflare.com |
| 2 | unpkg.com |
1 redirects
www.pukacreations.com
|
| 2 | cdn.jsdelivr.net |
www.pukacreations.com
|
| 1 | ajax.googleapis.com |
www.pukacreations.com
|
| 1 | kit.fontawesome.com |
www.pukacreations.com
|
| 1 | pukacreations.com | 1 redirects |
| 0 | cdn.jquery.app Failed |
www.pukacreations.com
|
| 67 | 8 |
This site contains links to these domains. Also see Links.
| Domain |
|---|
| www.facebook.com |
| www.instagram.com |
| wa.me |
| www.youtube.com |
| Subject Issuer | Validity | Valid | |
|---|---|---|---|
| pukacreations.com WE1 |
2026-09-08 - 2026-12-07 |
3mo | crt.sh |
| *.jsdelivr.net Sectigo Public Server Authentication CA DV R36 |
2026-04-22 - 2026-11-06 |
7mo | crt.sh |
| cdnjs.cloudflare.com WE1 |
2026-09-07 - 2026-12-06 |
3mo | crt.sh |
| fontawesome.com WE1 |
2026-08-12 - 2026-11-10 |
3mo | crt.sh |
| upload.video.google.com WE2 |
2026-09-18 - 2026-12-11 |
3mo | crt.sh |
This page contains 1 frames:
Primary Page:
https://www.pukacreations.com/
Frame ID: ABCBABE0D5F28C50AF3F8020B036841B
Requests: 67 HTTP requests in this frame
Screenshot
Go Pro
Only in urlscan Pro
Use the Visual Search feature to find pages with visually similar screenshots.
Click for more information
Free trials of urlscan Pro are available.
Page Title
Online Wholesale Products | Jewelry & Accessories - Puka CreationsPage URL History
Go Pro
Only in urlscan Pro
Search our real-time database of newly observed domains and
hostnames. Pivot on different attributes, and setup keyword alerts for
newly observed domains.
Click for more information
Free trials of urlscan Pro are available.
Show full URLs
-
http://pukacreations.com/
HTTP 307
https://pukacreations.com/ HTTP 301
https://www.pukacreations.com/ Page URL
Detected technologies
 Bootstrap
(UI frameworks)
Expand
Detected patterns
- <link[^>]* href=[^>]*?bootstrap(?:[^>]*?([0-9a-fA-F]{7,40}|[\d]+(?:.[\d]+(?:.[\d]+)?)?)|)[^>-]*?(?:\.min)?\.css
- (?:/|-)bootstrap(?:[^/]*?([0-9a-fA-F]{7,40}|[\d]+(?:\.[\d]+(?:\.[\d]+)?)?)|)[^/]*?(?:\.min)?\.js
 Laravel
(Web frameworks)
Expand
Detected patterns
 cdnjs
(CDN)
Expand
Detected patterns
- cdnjs\.cloudflare\.com
 Font Awesome
(Font scripts)
Expand
Detected patterns
- (?:F|f)o(?:n|r)t-?(?:A|a)wesome(?:.*?([0-9a-fA-F]{7,40}|[\d]+(?:.[\d]+(?:.[\d]+)?)?)|)
- \.fontawesome\.com/([0-9a-z]+).js
 Google Hosted Libraries
(CDN)
Expand
Detected patterns
- ajax\.googleapis\.com/ajax/libs/
 jQuery
(JavaScript libraries)
Expand
Detected patterns
- jquery
- /(\d+\.\d+\.\d+)/jquery(?!\.popupoverlay\.js|(?:\.[\w-]*)*fancybox)[/.-][^u]
 jsDelivr
(CDN)
Expand
Detected patterns
- cdn\.jsdelivr\.net
 OWL Carousel
(JavaScript libraries)
Expand
Detected patterns
- <link [^>]*href="[^"]+owl\.carousel(?:\.min)?\.css
- owl\.carousel.*\.js
 Unpkg
(CDN)
Expand
Detected patterns
- unpkg\.com/
 Popper
(Miscellaneous)
Expand
Detected patterns
- /popper(?:\.min)?\.js(?:/([0-9.]+))?
Page Statistics
4 Outgoing links
Go Pro
Only in urlscan Pro
Effortlessly use any on-page link as a pivot to discover other pages pointing to the exact same destination. Seamlessly trace both specific URLs and broader domains to uncover hidden connection networks and map out backlink relationships with ease.
Click for more information
Free trials of urlscan Pro are available.
These are links going to different origins than the main page.
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Page URL History
This captures the URL locations of the websites, including HTTP redirects and client-side redirects via JavaScript or Meta fields.
-
http://pukacreations.com/
HTTP 307
https://pukacreations.com/ HTTP 301
https://www.pukacreations.com/ Page URL
Redirected requests
There were HTTP redirect chains for the following requests:
Request Chain 18- https://unpkg.com/default-passive-events HTTP 302
- https://unpkg.com/default-passive-events@4.0.0/dist/index.umd.js
- https://www.pukacreations.com/cart_onload/ HTTP 301
- https://www.pukacreations.com/cart_onload
67 HTTP transactions
Go Pro
Only in urlscan Pro
Inspect WebSocket connections, examine POST data effortlessly, and track overlap counts in real time. Features live search and filtering across all HTTP output, complete with full response metadata for deep analysis.
Click for more information
Free trials of urlscan Pro are available.
0 data transactions
| Method Protocol |
Status | Resource Path |
Size x-fer |
Time Latency |
Type MIME-Type |
IP Location |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
|
GET H3 |
200 |
Primary Request
/
Show response
www.pukacreations.com/ Redirect Chain
|
204 KB 21 KB |
631ms
614ms |
Document
text/html |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
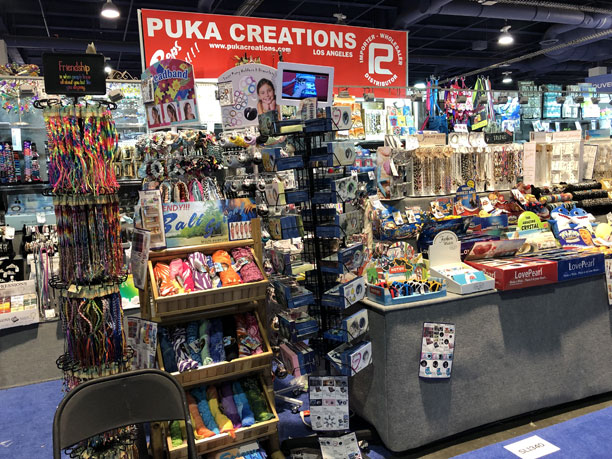
Tradeshow-PukaCreations-Wholesale.jpg
www.pukacreations.com/ |
127 KB 127 KB |
53ms
52ms |
Image
image/jpeg |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
bootstrap.min.css
cdn.jsdelivr.net/npm/bootstrap@4.6.2/dist/css/ |
158 KB 25 KB |
136ms
48ms |
Stylesheet
text/css |
104.17.207.5 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
owl.carousel.min.css
cdnjs.cloudflare.com/ajax/libs/OwlCarousel2/2.3.4/assets/ |
3 KB 1 KB |
104ms
58ms |
Stylesheet
text/css |
104.17.25.14 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
owl.theme.default.min.css
cdnjs.cloudflare.com/ajax/libs/OwlCarousel2/2.3.4/assets/ |
1013 B 945 B |
98ms
52ms |
Stylesheet
text/css |
104.17.25.14 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
jqueryscripttop.css
cdn.jquery.app/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
pe-icon-7-stroke.css
www.pukacreations.com/assets/frontend/css/ |
13 KB 3 KB |
51ms
50ms |
Stylesheet
text/css |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
style.css
www.pukacreations.com/assets/frontend/css/ |
52 KB 10 KB |
226ms
225ms |
Stylesheet
text/css |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
font-awesome.min.css
cdnjs.cloudflare.com/ajax/libs/font-awesome/4.7.0/css/ |
30 KB 6 KB |
96ms
52ms |
Stylesheet
text/css |
104.17.25.14 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
403 |
ef8d3d2e2f.js
kit.fontawesome.com/ |
0 0 |
284ms
186ms |
Script
text/plain |
104.18.40.68 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
logo.png
www.pukacreations.com/assets/frontend/images/ |
23 KB 24 KB |
53ms
52ms |
Image
image/png |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
speaker.png
www.pukacreations.com/assets/frontend/images/ |
1 KB 2 KB |
50ms
48ms |
Image
image/png |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
BBeach%20Items.png
www.pukacreations.com/uploads/sliderpic/ |
46 KB 46 KB |
89ms
88ms |
Image
image/png |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
email-decode.min.js
Show response
www.pukacreations.com/cdn-cgi/scripts/5c5dd728/cloudflare-static/ |
1 KB 1 KB |
46ms
45ms |
Script
application/javascript |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
jquery.min.js
Show response
ajax.googleapis.com/ajax/libs/jquery/3.7.1/ |
85 KB 30 KB |
197ms
64ms |
Script
text/javascript |
142.251.14.95 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
owl.carousel.min.js
Show response
cdnjs.cloudflare.com/ajax/libs/OwlCarousel2/2.3.4/ |
43 KB 11 KB |
57ms
51ms |
Script
application/javascript |
104.17.25.14 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
bootstrap.min.js
Show response
cdn.jsdelivr.net/npm/bootstrap@4.3.1/dist/js/ |
57 KB 16 KB |
51ms
45ms |
Script
application/javascript |
104.17.207.5 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
popper.min.js
Show response
cdnjs.cloudflare.com/ajax/libs/popper.js/1.14.7/umd/ |
21 KB 7 KB |
64ms
59ms |
Script
application/javascript |
104.17.25.14 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
custom.js
Show response
www.pukacreations.com/assets/frontend/js/ |
13 KB 3 KB |
231ms
225ms |
Script
text/javascript |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
index.umd.js
Show response
unpkg.com/default-passive-events@4.0.0/dist/ Redirect Chain
|
1 KB 996 B |
57ms
56ms |
Script
text/javascript |
104.18.1.22 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
lazysizes.min.js
Show response
cdnjs.cloudflare.com/ajax/libs/lazysizes/5.3.2/ |
8 KB 4 KB |
58ms
54ms |
Script
application/javascript |
104.17.25.14 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
fontawesome-webfont.woff2
cdnjs.cloudflare.com/ajax/libs/font-awesome/4.7.0/fonts/ |
75 KB 76 KB |
179ms
178ms |
Font
application/octet-stream |
104.17.25.14 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
79647825658-Plush%20Wallets.webp
www.pukacreations.com/uploads/featured_images/ |
27 KB 27 KB |
267ms
264ms |
Image
text/plain |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
72532325634-Sea%20Life%20Bling%20Key%20Chain.webp
www.pukacreations.com/uploads/featured_images/ |
27 KB 27 KB |
260ms
256ms |
Image
text/plain |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
84339325559-Gemstone%20Sport%20Bracelets.webp
www.pukacreations.com/uploads/featured_images/ |
22 KB 23 KB |
229ms
224ms |
Image
text/plain |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
58733325542-Magneti%20Hematite.webp
www.pukacreations.com/uploads/featured_images/ |
26 KB 26 KB |
257ms
251ms |
Image
text/plain |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
19651015659-Jumbo%20Maltose%20Banana.webp
www.pukacreations.com/uploads/featured_images/ |
22 KB 23 KB |
53ms
47ms |
Image
text/plain |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
84496213594-Light%20Up%20Spinner%20and%20Press%20Fidget%20Toy.webp
www.pukacreations.com/uploads/featured_images/ |
26 KB 26 KB |
59ms
53ms |
Image
text/plain |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
52304315727-Jumbo-Squeeze-Highland-Cow.webp
www.pukacreations.com/uploads/featured_images/ |
23 KB 23 KB |
70ms
64ms |
Image
text/plain |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
86408813440-Jumbo%20Squishy%20Coin.webp
www.pukacreations.com/uploads/featured_images/ |
28 KB 29 KB |
65ms
59ms |
Image
text/plain |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
58137813570-Halloween%20Maltose.webp
www.pukacreations.com/uploads/featured_images/ |
29 KB 29 KB |
64ms
58ms |
Image
text/plain |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
872508category-02109-1.webp
www.pukacreations.com/uploads/category_images/ |
10 KB 10 KB |
57ms
51ms |
Image
text/plain |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
54889306190_150px.jpg
www.pukacreations.com/uploads/category_images/ |
5 KB 6 KB |
63ms
58ms |
Image
image/jpeg |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
45956308255-Guardian-Angels-Pendant_150px_2.jpg
www.pukacreations.com/uploads/category_images/ |
5 KB 6 KB |
64ms
59ms |
Image
image/jpeg |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
885602evil-eye-bracelets_150px.jpg
www.pukacreations.com/uploads/category_images/ |
8 KB 8 KB |
227ms
221ms |
Image
image/jpeg |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
73748613673_leather_150px.jpg
www.pukacreations.com/uploads/category_images/ |
7 KB 8 KB |
58ms
52ms |
Image
image/jpeg |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
85445236477_150px.jpg
www.pukacreations.com/uploads/category_images/ |
9 KB 10 KB |
69ms
64ms |
Image
image/jpeg |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
30210710818-Turtle-Leather-Keychain-and-Coin-Purse_150px_1.jpg
www.pukacreations.com/uploads/category_images/ |
8 KB 8 KB |
251ms
245ms |
Image
image/jpeg |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
74758539010_150px.jpg
www.pukacreations.com/uploads/category_images/ |
7 KB 7 KB |
69ms
64ms |
Image
image/jpeg |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
99479101013.jpg
www.pukacreations.com/uploads/category_images/ |
19 KB 19 KB |
250ms
245ms |
Image
image/jpeg |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
29196402478-Closeout%20Fashion%20Pony%20Tail%20and%20Bracelets_36-18%20copy.jpg
www.pukacreations.com/uploads/category_images/ |
25 KB 25 KB |
62ms
57ms |
Image
image/jpeg |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
61678000917.jpg
www.pukacreations.com/uploads/category_images/ |
37 KB 37 KB |
246ms
241ms |
Image
image/jpeg |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
51414739935-Closeout%20Sand%20Dollar%20Rings_36-36%20copy.webp
www.pukacreations.com/uploads/category_images/ |
13 KB 13 KB |
61ms
56ms |
Image
text/plain |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
440159category-13396-1.webp
www.pukacreations.com/uploads/category_images/ |
10 KB 10 KB |
68ms
63ms |
Image
text/plain |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
649263sollbreeze1.jpg
www.pukacreations.com/uploads/category_images/ |
26 KB 27 KB |
68ms
63ms |
Image
image/jpeg |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
39513613192-Cute-Sticker.webp
www.pukacreations.com/uploads/featured_images/ |
45 KB 46 KB |
61ms
57ms |
Image
text/plain |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
895192004-Nck-09194-Genuine-Pearl-with-Japanese-Beads.webp
www.pukacreations.com/uploads/featured_images/ |
22 KB 23 KB |
230ms
226ms |
Image
text/plain |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
62859013543-Triple-Genuine-Pearl-Anklet.webp
www.pukacreations.com/uploads/featured_images/ |
12 KB 12 KB |
62ms
58ms |
Image
text/plain |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
69937812164-Triple-Genuine-Pearl-Bracelets.webp
www.pukacreations.com/uploads/featured_images/ |
13 KB 14 KB |
228ms
225ms |
Image
text/plain |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
92880904571-Triple-Genuine-Pearl-Necklaces.webp
www.pukacreations.com/uploads/featured_images/ |
11 KB 12 KB |
224ms
220ms |
Image
text/plain |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
23250903222-Pearl-Necklaces.webp
www.pukacreations.com/uploads/featured_images/ |
10 KB 11 KB |
60ms
57ms |
Image
text/plain |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
65131103017-Pearl-Bracelets.webp
www.pukacreations.com/uploads/featured_images/ |
13 KB 13 KB |
60ms
57ms |
Image
text/plain |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
32577611723-Paracord-Bracelets.webp
www.pukacreations.com/uploads/featured_images/ |
47 KB 48 KB |
66ms
63ms |
Image
text/plain |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
82440400474-Survival-Bracelets.webp
www.pukacreations.com/uploads/featured_images/ |
37 KB 37 KB |
60ms
57ms |
Image
text/plain |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
left.png
www.pukacreations.com/assets/frontend/images/ |
708 B 1 KB |
49ms
49ms |
Image
image/png |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
right.png
www.pukacreations.com/assets/frontend/images/ |
752 B 1 KB |
50ms
49ms |
Image
image/png |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
KKids%20Items.png
www.pukacreations.com/uploads/sliderpic/ |
40 KB 41 KB |
54ms
52ms |
Image
image/png |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
AAssorted.png
www.pukacreations.com/uploads/sliderpic/ |
48 KB 49 KB |
54ms
53ms |
Image
image/png |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
AApparel.jpg
www.pukacreations.com/uploads/sliderpic/ |
35 KB 36 KB |
235ms
234ms |
Image
image/jpeg |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
HHome%20Decor.png
www.pukacreations.com/uploads/sliderpic/ |
30 KB 30 KB |
227ms
226ms |
Image
image/png |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
AAccessories.png
www.pukacreations.com/uploads/sliderpic/ |
37 KB 37 KB |
216ms
215ms |
Image
image/png |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
Jewelry.png
www.pukacreations.com/uploads/pukahomepage/ |
158 KB 158 KB |
227ms
226ms |
Image
image/png |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
count
Show response
www.pukacreations.com/ |
1 B 1 KB |
301ms
300ms |
XHR
text/html |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
500 |
cart_count
Show response
www.pukacreations.com/ |
33 B 1 KB |
294ms
293ms |
XHR
application/json |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
cart_onload
Show response
www.pukacreations.com/ Redirect Chain
|
10 B 1 KB |
304ms
303ms |
XHR
application/json |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
favicon.png
www.pukacreations.com/assets/frontend/images/ |
1 KB 2 KB |
53ms
52ms |
Other
image/png |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
HHome%20Decor.png
www.pukacreations.com/uploads/sliderpic/ |
30 KB 0 |
0ms
0ms |
Image
image/png |
172.67.212.177 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||


























Failed requests
These URLs were requested, but there was no response received. You will also see them in the list above.
- Domain
- cdn.jquery.app
- URL
- https://cdn.jquery.app/jqueryscripttop.css?v=1.2.3
Verdicts & Comments Add Verdict or Comment
19 JavaScript Window variables
Go Pro
Only in urlscan Pro
Inspect and pivot on JavaScript variables, identifiers, and other key site metadata data with urlscan Pro. Reveal and search on client-side frameworks, runtime variables, and custom values.
Click for more information
Free trials of urlscan Pro are available.
These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.
function| requestResize function| gtag object| dataLayer function| generateCaptcha function| $ function| jQuery function| openNav function| closeNav object| bootstrap function| Popper object| lazySizes function| showDiv5 function| ShowPincodepopup function| HidePincodepopup function| SelectMale function| SelectFemale function| getCategoryFilter function| addToCart function| rdmore2 Cookies
Go Pro
Only in urlscan Pro
Review, search, and pivot on browser cookies and persistence site data to see how a site tracks users and keeps sessions alive across visits.
Click for more information
Free trials of urlscan Pro are available.
Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.
| Domain/Path | Expires | Name / Value | |||
|---|---|---|---|---|---|
| www.pukacreations.com/ | 1970-01-21 17:26:45 |
Name: XSRF-TOKEN Value: eyJpdiI6IjdGemdENUtJck9sZm5Kc0hDd3BtbEE9PSIsInZhbHVlIjoiY2VkaThcL0t0ZjRqd201RUpIWTF4VmNKcGpCbDJRRDZjMWoxTVNJYTVzWmUzRjlaekIyTllGVVJybGZqcGpuYnUiLCJtYWMiOiI0ZGZlNWZmNWNkYmJhYWU0NGIyOGQ4MGVmMzY2MWY1NWMwOTc4YjkzNWYyMDNmNTFlNTM1YWJkNjgwNzhmYjFhIn0%3D |
|||
| www.pukacreations.com/ | 1970-01-21 17:26:45 |
Name: laravel_session Value: eyJpdiI6IjRoWkJUT215RmVLTWZnc1Y1QTUwUXc9PSIsInZhbHVlIjoiU1NZcytja3ZNNVZHeWFMcVwva0FZR1orZitRYW83Rmo0VExhYTZ4T2QzU1h3MWZaNXh4TTJvVDdidHpmTkZOSjkiLCJtYWMiOiJhOGRkNzVkNjBhMGEzMzA1OTYwYWUwNjAzMDBmYjRmZmZhYWYyOTIxMjU3MGI3NzRjNGVlNTA4MGFhMDZmNGIxIn0%3D |
50 Console Messages
A page may trigger messages to the console to be logged. These are often error messages about being unable to load a resource or execute a piece of JavaScript. Sometimes they also provide insight into the technology behind a website.
| Source | Level | URL Text |
|---|
Security Headers
This page lists any security headers set by the main page. If you want to understand what these mean and how to use them, head on over to this page
| Header | Value |
|---|---|
| Strict-Transport-Security | max-age=31536000; includeSubDomains |
| X-Content-Type-Options | nosniff |
| X-Frame-Options | DENY |
| X-Xss-Protection | 1; mode=block |
Indicators
This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.
ajax.googleapis.com
cdn.jquery.app
cdn.jsdelivr.net
cdnjs.cloudflare.com
kit.fontawesome.com
pukacreations.com
unpkg.com
www.pukacreations.com
cdn.jquery.app
104.17.207.5
104.17.25.14
104.18.1.22
104.18.40.68
142.251.14.95
172.67.212.177
02d66b40be3599abcb92f51cd1146ba940e93206c2006f7568ca9c08795eb4a1
058ef7eeedf9727ae4cb7548b3816bc786d43a4415b75cd33552369aaa24d16d
068feb155fd323339673dbe7ba1167327a8d3299fab997de3e91943e2b205a8a
0a34a87842c539c1f4feec56bba982fd596b73500046a6e6fe38a22260c6577b
0c5c2f76baabd662c5f96c2d278744500a9b7fd4e048103a1027e2618375bdec
0e43444a6f4cee293decf113e3da5bede38e4a4e57b6c3a52d92eda9f16182be
144e6863621f51b6037171a61ab24d77a9abe71298c1c3b751789b134cd7cff7
19e532beecd7203d85da17449c4910e8803f9e0bff54a3e564f6f012f8b460d6
1f3a42737cda5c0945e6dfe7bb1527aaf62896a33fa61d497b3ec7de27cfc32b
1fc1aadc494d6571c2c74ff46514f0a638697ac6d9221e3d26bbaf4c3c3cf60e
2505fa2c021861f17df4ffedfa0700dd452bc5686053a0249634897f96dc2cc8
2595496fe48df6fcf9b1bc57c29a744c121eb4dd11566466bc13d2e52e6bbcc8
2733c1515fcefee004fca7ea89317a87619bde5ec1111a77fd41323d0d478fb5
29b11052ce631e23725d099582cdc66857374c0c924453057d6d78c4f3b682e2
2adefcbc041e7d18fcf2d417879dc5a09997aa64d675b7a3c4b6ce33da13f3fe
2f69b20ac2980f1262c2fa11822b082b50723215673f5ea0df13a129dbd2c92d
39161f753328782ae72f5f23ec38ea2eec1ce2f3aed3c19c98c9e5986417bf7f
3d9120fa621da6d613c1698b7014ec6bdf4620366e8f2b7b547059f4b6f6272b
427c02a0cb880fe385830ca3010d5b240b208ee0d86dc0216d2f90b6c3e1b5d1
4679c5570c936ee94097f51c6d34ee2d66d4becbc68de88f8018cb0fcf8a589f
5184af1386f0cee7fbc6b4697afb0b647c468fd36822a5e5dd1fc81a0d7d81c3
521410e1fc44780061e09adc980275fb5ea277fd5d9e538454214ec4379ff4bc
522fe71421774ee17073f80d2da198d975087b340919c9dbbf7b6093fb1af503
53d58a7f50a9f2c152b2b6933f19a152e1e4f9b8fb9f905ba4c664edd04cc9bc
5572fcebcc1d2e5448c023cfe4b6aa1be989a3e02bfae58ef85c870328f9d198
5a07644c57c0fb7870ae3fc92bf37506d195ca083a92324ed41457e677924dc5
5feceb66ffc86f38d952786c6d696c79c2dbc239dd4e91b46729d73a27fb57e9
65bc31aecc40f05c48c82f09198b0d857f69e5650fb2f7f20e4add4d5829f0b8
66f3a07e1fa9b64a686b66381e4458dbc8abf3dbbff954720c4eec07b84411c2
7633eb41808c6d75da0f4920c9e7d619b38ef5f86e787f0586a0caea1a151363
799aeb25cc0373fdee0e1b1db7ad6c2f6a0e058dfadaa3379689f583213190bd
7b5e0c07750a641453dcd4edc48e794e07007c8870c0165cfa99319615dd25ea
81a6e25fc23bcfcc466426e95f3a6999739feac76f652fac471bff8119d2e556
844b3f0b3470f0b8a4d2e99cfcf69389e0efc62285e4667089668bce3156d4c4
8651b13cd80122b7b2bacd468464b8ba2e21cd4063c472407aacd4cd817b511b
924b0dc630d1c5dff9fa31aead9509775b1d476bfe0a5ac2977b2f11205a26ac
93063ad814cded504d142c7fcffeda7b6b3cad80cbb8b786ec5a3603eeef7f8a
94d93306b6f1703c3828dfb6fa122058f0313d4796f3326350832646aeaf3502
967ea42194267e0291d4571a5eab9a89aea0cfe01f6552eedd6db38f338c271a
9bf1754c03c8f0229fa53e484833f523164c972817142e8e95358d6b50cdc826
9ea9d6320c836c87ff0c3ca122b36a7ac26fda439f7e58b584727ebbfc6685c8
a1ccde96aae572547636db6602544e94aee22eeb25e94693facdc8d63d622dee
a2349077ba1169b2eb53b3ddc30a1314cbc53de662960275b6da87f668a2baec
a240b68dc5e8f6953fb051d6b99cff94a61f54ae799323d3b0af092a334f54a3
a53c43f834b32309b084ea9314df8307e9c78cee2202c6e07f216ae4ae5b704d
a6616a47159e31eda23af14e0623aee90f9258907eae7dfe63520b35a992100e
a9c639d15612a7c90662097ff0b90d9d81f612bf5e210b5968a63004edd58e2f
b48f5370771436893d40324bbcb45e201b83a5f02106f39882171e7679d2c5c1
bd69dc2c8d38977b0f16a8ad3f7eb906b923eeb6e1f25b1a03d950f46f4fd32d
c2b7f1d4912a4b826b0d55c2b9826ed782362e38a29cda91bcd49008c01f2924
ccbe21c39849a58552f0e17f83b513a0baacb6d7fe66fb1eee72577372d3da53
ce8f46b1e1f5879414527741205a37ba06639589849ad76c137822ff5f3ae9e1
d32207236eddcf4218abe357c8e7009a82a9fae4ad522363ce42a86fbd14b65a
e5fefacf4c64997f9e0b4a22524cb4f34e9c893585421d91ceafeb92050d9545
e62a79422284523ab2a6301ea208dfd2da5e64592600036958d7652b52f3870f
e842c101bc4dba64c800880b7e69efe18932fed6a3632f9440db7321c64d54b0
eb0f3680290ed56cbec4f99bf48d01e0d2d72384bb748007c22ceeda07a1b354
ed4ad9d4da92ce3a61df55b277195598c5e540836e790d39d4c8610fe09f6bd8
ee817abee39385c2dbabed7da40c9ea5cc90214c467f700669b9aec30b7f8139
f43d8726a62ffc009dfc921db9699371f7ad5fd3a91de8ee560d9cef4e5d2096
f82bab660491fa7593a16af10f1bc2b8728e383bcd53ace98c6d072954dd3f0c
f886516f3d41e9e7bd994c7f7a39a89cafae9483f90396cb0ddeafe8d1ea5e72
f8f8092a000cb7ef087115320d57c08f3c7171ca85d6d122a1eefcd35f761532
fc9a93dd241f6b045cbff0481cf4e1901becd0e12fb45166a8f17f95823f0b1a