Summary

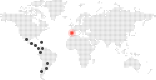
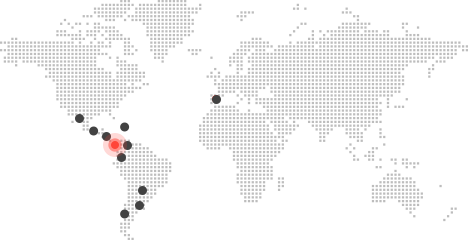
This website contacted 32 IPs in 7 countries across 26 domains to perform 217 HTTP transactions. The main IP is 2a02:26f0:3500:12::1730:178a, located in Frankfurt am Main, Germany and belongs to AKAMAI-ASN1 Akamai International B.V., NL. The main domain is los40.com.pa. 10yr old
TLS certificate: Issued by YE1 on September 21st 2026. Valid for: 3mo.
This is the only time los40.com.pa was scanned on urlscan.io!

Domain & IP information

IP Address AS Autonomous System
39 2a02:26f0:350... 2a02:26f0:3500:12::1730:178a 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.)
13 2a02:26f0:350... 2a02:26f0:3500:12::1730:1799 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.)
13 199.232.198.133 199.232.198.133 54113 (FASTLY) (FASTLY - Fastly)
22 2001:4860:482... 2001:4860:4826:400:: 15169 (GOOGLE) (GOOGLE - Google LLC)
2 2600:9000:28e... 2600:9000:28eb:1000:5:b7cc:d3c0:93a1 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
20 2a02:26f0:278... 2a02:26f0:2780:a9e::1e80 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.)
2 178.33.150.172 178.33.150.172 16276 (OVH OVH SAS) (OVH OVH SAS)
1 142.251.14.155 142.251.14.155 15169 (GOOGLE) (GOOGLE - Google LLC)
6 142.251.110.94 142.251.110.94 15169 (GOOGLE) (GOOGLE - Google LLC)
11 142.251.154.4 142.251.154.4 15169 (GOOGLE) (GOOGLE - Google LLC)
1 2 52.30.159.196 52.30.159.196 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
3 9 142.251.110.154 142.251.110.154 15169 (GOOGLE) (GOOGLE - Google LLC)
6 2a00:1450:400... 2a00:1450:4001:c15::95 15169 (GOOGLE) (GOOGLE - Google LLC)
27 142.251.155.119 142.251.155.119 15169 (GOOGLE) (GOOGLE - Google LLC)
6 2a00:1450:400... 2a00:1450:4001:c25::77 15169 (GOOGLE) (GOOGLE - Google LLC)
5 52.17.233.147 52.17.233.147 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
2 63.140.62.120 63.140.62.120 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
4 63.140.62.200 63.140.62.200 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
6 2001:4860:484... 2001:4860:4841:400:: 15169 (GOOGLE) (GOOGLE - Google LLC)
2 3.174.46.14 3.174.46.14 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
2 2 142.251.14.156 142.251.14.156 15169 (GOOGLE) (GOOGLE - Google LLC)
1 63.140.62.210 63.140.62.210 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
2 2001:4860:482... 2001:4860:482b:400:: 15169 (GOOGLE) (GOOGLE - Google LLC)
2 3 192.173.31.109 192.173.31.109 13360 (TRITONDIG...) (TRITONDIGITAL - Triton Digital)
2 3.173.128.89 3.173.128.89 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
2 51.138.12.100 51.138.12.100 8075 (MICROSOFT...) (MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation)
1 2600:9000:20a... 2600:9000:20ab:ea00:1:ef39:a380:93a1 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 35.71.131.137 35.71.131.137 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 63.140.62.139 63.140.62.139 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 18.238.243.129 18.238.243.129 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
2 2 103.231.98.107 103.231.98.107 62713 (AS-PUBMATIC) (AS-PUBMATIC - PubMatic)
1 1 18.245.46.103 18.245.46.103 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
3 172.217.113.4 172.217.113.4 15169 (GOOGLE) (GOOGLE - Google LLC)
1 2a00:1450:400... 2a00:1450:4001:c0f::5f 15169 (GOOGLE) (GOOGLE - Google LLC)
217 32
Apex Domain
Subdomains
Transfer
56 youtube.com
www.youtube.com — Cisco Umbrella Rank: 115 10yr old
2 MB
41 los40.com.pa
los40.com.pa 10yr old
smetrics.los40.com.pa 1mo old
544 KB
20 adobedtm.com
assets.adobedtm.com — Cisco Umbrella Rank: 291 13yr old
171 KB
17 doubleclick.net 5 redirects
googleads.g.doubleclick.net — Cisco Umbrella Rank: 75 10yr old
static.doubleclick.net — Cisco Umbrella Rank: 285 10yr old
cm.g.doubleclick.net — Cisco Umbrella Rank: 353 10yr old
1 KB
13 los40.com
los40.com — Cisco Umbrella Rank: 499487 10yr old
184 KB
10 googleapis.com
jnn-pa.googleapis.com — Cisco Umbrella Rank: 352 5yr old
imasdk.googleapis.com — Cisco Umbrella Rank: 633 10yr old
157 KB
8 demdex.net 1 redirects
dpm.demdex.net — Cisco Umbrella Rank: 380 10yr old
prisacom.demdex.net — Cisco Umbrella Rank: 92935 9yr old
adobedc.demdex.net — Cisco Umbrella Rank: 3206 7yr old
9 KB
6 ytimg.com
i.ytimg.com — Cisco Umbrella Rank: 134 10yr old
34 KB
6 google.com
www.google.com — Cisco Umbrella Rank: 5 14yr old
72 KB
6 gstatic.com
fonts.gstatic.com — Cisco Umbrella Rank: 33 10yr old
39 KB
6 prisamedia.com
player.prisamedia.com — Cisco Umbrella Rank: 111515 2yr old
92 KB
4 omtrdc.net
prisacom.tt.omtrdc.net — Cisco Umbrella Rank: 106643 9yr old
1 KB
4 privacy-center.org
sdk.privacy-center.org — Cisco Umbrella Rank: 3112 9yr old
151 KB
3 prisaradio.com
recursosweb.prisaradio.com — Cisco Umbrella Rank: 253878 10yr old
12 MB
3 adobedc.net
dcs.adobedc.net — Cisco Umbrella Rank: 2765 7yr old
edge.adobedc.net — Cisco Umbrella Rank: 2177 7yr old
1 KB
3 amazon-adsystem.com
c.amazon-adsystem.com — Cisco Umbrella Rank: 572 13yr old
config.aps.amazon-adsystem.com — Cisco Umbrella Rank: 1037 4yr old
97 KB
3 streamtheworld.com 2 redirects
playerservices.live.streamtheworld.com — Cisco Umbrella Rank: 18408 10yr old
1 KB
2 pubmatic.com 2 redirects
image6.pubmatic.com — Cisco Umbrella Rank: 970 10yr old
551 B
2 prisasd.com
fapi-top.prisasd.com — Cisco Umbrella Rank: 114224 10yr old
2 KB
2 socy.es
prra.spxl.socy.es — Cisco Umbrella Rank: 145998 6yr old
11 KB
2 prisa.com
cmp.prisa.com — Cisco Umbrella Rank: 101129 5yr old
static.prisa.com — Cisco Umbrella Rank: 87701 3yr old
31 KB
1 adswizz.com 1 redirects
synchroscript.deliveryengine.adswizz.com — Cisco Umbrella Rank: 4272 9yr old
438 B
1 adsrvr.org
match.adsrvr.org — Cisco Umbrella Rank: 515 10yr old
149 B
1 listenlive.co
sdk.listenlive.co — Cisco Umbrella Rank: 122112 10yr old
364 KB
1 googlesyndication.com
pagead2.googlesyndication.com — Cisco Umbrella Rank: 126 10yr old
0 adnxs.com Failed
ib.adnxs.com Failed 10yr old
217 26
Domain Requested by
56 www.youtube.com los40.com.pa
www.youtube.com
39 los40.com.pa los40.com.pa
20 assets.adobedtm.com los40.com.pa
assets.adobedtm.com
13 los40.com los40.com.pa
9 jnn-pa.googleapis.com www.youtube.com
9 googleads.g.doubleclick.net 3 redirects www.youtube.com
6 i.ytimg.com www.youtube.com
6 www.google.com www.youtube.com
6 static.doubleclick.net www.youtube.com
6 dpm.demdex.net 1 redirects los40.com.pa
6 fonts.gstatic.com www.youtube.com
6 player.prisamedia.com los40.com.pa
player.prisamedia.com
4 prisacom.tt.omtrdc.net assets.adobedtm.com
4 sdk.privacy-center.org cmp.prisa.com
sdk.privacy-center.org
3 recursosweb.prisaradio.com los40.com.pa
3 playerservices.live.streamtheworld.com 2 redirects los40.com.pa
2 image6.pubmatic.com 2 redirects
2 dcs.adobedc.net los40.com.pa
2 c.amazon-adsystem.com los40.com.pa
c.amazon-adsystem.com
2 cm.g.doubleclick.net 2 redirects
2 smetrics.los40.com.pa assets.adobedtm.com
los40.com.pa
2 fapi-top.prisasd.com player.prisamedia.com
2 prra.spxl.socy.es los40.com.pa
prra.spxl.socy.es
1 imasdk.googleapis.com sdk.listenlive.co
1 synchroscript.deliveryengine.adswizz.com 1 redirects
1 config.aps.amazon-adsystem.com c.amazon-adsystem.com
1 edge.adobedc.net assets.adobedtm.com
1 match.adsrvr.org los40.com.pa
1 sdk.listenlive.co player.prisamedia.com
1 adobedc.demdex.net assets.adobedtm.com
1 prisacom.demdex.net assets.adobedtm.com
1 pagead2.googlesyndication.com los40.com.pa
1 static.prisa.com los40.com.pa
1 cmp.prisa.com los40.com.pa
0 ib.adnxs.com Failed los40.com.pa
217 35
Subject Issuer Validity Valid
los40.com.pa
YE1
2026-09-21 -
2026-12-20
3mo crt.sh
prisaradiolos40.web.arc-cdn.net
YR1
2026-08-18 -
2026-11-16
3mo crt.sh
*.prisamedia.com
YR1
2026-09-01 -
2026-11-30
3mo crt.sh
*.prisa.com
YR1
2026-08-07 -
2026-11-05
3mo crt.sh
*.google.com
WR2
2026-09-18 -
2026-12-11
3mo crt.sh
sdk.privacy-center.org
Amazon RSA 2048 M01
2026-08-17 -
2027-03-02
7mo crt.sh
assets.adobedtm.com
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2026-09-23 -
2027-04-09
7mo crt.sh
*.spxl.socy.es
YR1
2026-08-23 -
2026-11-21
3mo crt.sh
*.g.doubleclick.net
WE2
2026-09-18 -
2026-12-11
3mo crt.sh
*.gstatic.com
WE2
2026-09-18 -
2026-12-11
3mo crt.sh
*.prisasd.com
YR1
2026-08-14 -
2026-11-12
3mo crt.sh
*.doubleclick.net
WE2
2026-09-18 -
2026-12-11
3mo crt.sh
edgestatic.com
WR2
2026-09-18 -
2026-12-11
3mo crt.sh
*.demdex.com
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2026-09-24 -
2027-04-10
7mo crt.sh
smetrics.los40.com.pa
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2026-08-31 -
2027-03-17
7mo crt.sh
*.tt.omtrdc.net
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2026-02-17 -
2027-03-20
1yr crt.sh
upload.video.google.com
WR2
2026-09-18 -
2026-12-11
3mo crt.sh
adobedc.demdex.net
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2025-10-25 -
2026-11-25
1yr crt.sh
c.amazon-adsystem.com
Amazon RSA 2048 M04
2026-09-20 -
2027-04-05
7mo crt.sh
dcs.adobedc.net
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2026-09-30 -
2027-04-16
7mo crt.sh
*.listenlive.co
Amazon RSA 2048 M01
2026-09-07 -
2027-03-23
7mo crt.sh
*.adsrvr.org
GlobalSign GCC R3 DV TLS CA 2020
2026-03-04 -
2027-04-02
1yr crt.sh
edge.adobedc.net
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2025-10-24 -
2026-11-24
1yr crt.sh
config.aps.amazon-adsystem.com
Amazon RSA 2048 M04
2025-11-23 -
2026-12-22
1yr crt.sh
*.prisaradio.com
YR2
2026-08-30 -
2026-11-28
3mo crt.sh

This page contains 5 frames:

Primary Page: https://los40.com.pa/
Frame ID: 2B9FF71F973DE93465A5588CEC78C76B
Requests: 110 HTTP requests in this frame

Frame: https://www.youtube.com/embed/fRIhCiUVaKs?enablejsapi=1
Frame ID: 8D1090830A2A110D7D9F4C674ECDAB5A
Requests: 32 HTTP requests in this frame

Frame: https://www.youtube.com/embed/s3a4OQR-10M?enablejsapi=1
Frame ID: CCE29882A3603B28EEB88DC68D18BA20
Requests: 32 HTTP requests in this frame

Frame: https://www.youtube.com/embed/_1W51TfwOEA?enablejsapi=1
Frame ID: B4208118DF2BFEEEAC698934DD32A4FE
Requests: 32 HTTP requests in this frame

Frame: https://prisacom.demdex.net/dest5.html?d_nsid=0
Frame ID: 02223A7905EFB8C6307690911C30BB5D
Requests: 7 HTTP requests in this frame

Screenshot Go Pro

Only in urlscan Pro

Use the Visual Search feature to find pages with visually similar screenshots.
Click for more information
Free trials of urlscan Pro are available.

Page Title

LOS40 Panamá: noticias musicales y todos los éxitos

Page URL History Go Pro

Only in urlscan Pro

Search our real-time database of newly observed domains and hostnames. Pivot on different attributes, and setup keyword alerts for newly observed domains.
Click for more information
Free trials of urlscan Pro are available.
Show full URLs

  1. http://los40.com.pa/ HTTP 307
    https://los40.com.pa/ Page URL

Detected technologies

(Video players)
Overall confidence: 100%
Detected patterns
  • \.youtube\.com/

(Segmentation)
Overall confidence: 100%
Detected patterns

(Advertising)
Overall confidence: 100%
Detected patterns
  • \.amazon-adsystem\.com

(Cookie compliance)
Overall confidence: 100%
Detected patterns
  • sdk\.privacy-center\.org/.*/loader\.js

(Advertising)
Overall confidence: 100%
Detected patterns
  • \.doubleclick\.net

(Advertising)
Overall confidence: 100%
Detected patterns
  • googlesyndication\.com/

(Advertising)
Overall confidence: 100%
Detected patterns
  • \.adsrvr\.org/

Page Statistics

217
Requests

93 %
HTTPS

32 %
IPv6

26
Domains

35
Subdomains

32
IPs

7
Countries

16210 kB
Transfer

41533 kB
Size

25
Cookies

Page URL History

This captures the URL locations of the websites, including HTTP redirects and client-side redirects via JavaScript or Meta fields.

  1. http://los40.com.pa/ HTTP 307
    https://los40.com.pa/ Page URL

Redirected requests

There were HTTP redirect chains for the following requests:

Request Chain 74
  • https://dpm.demdex.net/id?d_visid_ver=5.4.0&d_fieldgroup=MC&d_rtbd=json&d_ver=2&d_verify=1&d_orgid=2387401053DB208C0A490D4C%40AdobeOrg&d_nsid=0&ts=1790881025393 HTTP 302
  • https://dpm.demdex.net/id/rd?d_visid_ver=5.4.0&d_fieldgroup=MC&d_rtbd=json&d_ver=2&d_verify=1&d_orgid=2387401053DB208C0A490D4C%40AdobeOrg&d_nsid=0&ts=1790881025393
Request Chain 77
  • https://googleads.g.doubleclick.net/pagead/id HTTP 302
  • https://googleads.g.doubleclick.net/pagead/id?slf_rd=1
Request Chain 81
  • https://googleads.g.doubleclick.net/pagead/id HTTP 302
  • https://googleads.g.doubleclick.net/pagead/id?slf_rd=1
Request Chain 84
  • https://googleads.g.doubleclick.net/pagead/id HTTP 302
  • https://googleads.g.doubleclick.net/pagead/id?slf_rd=1
Request Chain 130
  • https://cm.g.doubleclick.net/pixel?google_nid=adobe_dmp&google_cm&gdpr=0&gdpr_consent=&google_hm=NzA2MTUwMTUxODUzMDgxMTYxNjI3MDUyNTc0Mzg4NzEzNjA4NDE= HTTP 302
  • https://cm.g.doubleclick.net/pixel?google_nid=adobe_dmp&google_cm=&gdpr=0&gdpr_consent=&google_hm=NzA2MTUwMTUxODUzMDgxMTYxNjI3MDUyNTc0Mzg4NzEzNjA4NDE=&google_tc= HTTP 302
  • https://dpm.demdex.net/ibs:dpid=771&dpuuid=CAESEPNJjf-6UxETQKeV303PRbM&google_cver=1?gdpr=0&gdpr_consent=
Request Chain 133
  • https://playerservices.live.streamtheworld.com/api/idsync.js?stationId=&gdpr=0&gdpr_consent=undefined HTTP 302
  • https://playerservices.live.streamtheworld.com/api/idsync.js?stationId=&gdpr=0&gdpr_consent=undefined&bounce=true
Request Chain 156
  • https://image6.pubmatic.com/AdServer/UCookieSetPug?p=166334&rd=https%3A%2F%2Fdpm.demdex.net%2Fibs%3Adpid=19566%26dpuuid=%23PM_USER_ID HTTP 302
  • https://image6.pubmatic.com/AdServer/UCookieSetPug?p=166334&rd=https%3A%2F%2Fdpm.demdex.net%2Fibs%3Adpid=19566%26dpuuid=%23PM_USER_ID&rdf=1 HTTP 302
  • https://dpm.demdex.net/ibs:dpid=19566&dpuuid=2D34D10C-38AF-4AA3-ACA5-B11BDA5E79D1
Request Chain 178
  • https://synchroscript.deliveryengine.adswizz.com/getUID?curl=https%3A%2F%2Fdpm.demdex.net%2Fibs%3Adpid%3D175765%26dpuuid%3D%24%7BUID%7D HTTP 302
  • https://dpm.demdex.net/ibs:dpid=175765&dpuuid=ea796336d9dc2cd9f6ef31d5042f4773
Request Chain 190
  • https://playerservices.live.streamtheworld.com/api/getuuid?redir=https%3A%2F%2Fdpm.demdex.net%2Fibs%3Adpid%3D963840%26dpuuid%3D%40UUID%40 HTTP 302
  • https://dpm.demdex.net/ibs:dpid=963840&dpuuid=9c1a0b31-7301-41fb-8f2a-844137adf9ca

217 HTTP transactions Go Pro

Only in urlscan Pro

Inspect WebSocket connections, examine POST data effortlessly, and track overlap counts in real time. Features live search and filtering across all HTTP output, complete with full response metadata for deep analysis.
Click for more information
Free trials of urlscan Pro are available.

0 data transactions

Method
Protocol
Status Resource
Path
Size
x-fer
Time
Latency
Type
MIME-Type
IP
Location
GET
H2
200
Primary Request / Show response
los40.com.pa/
Redirect Chain
  • http://los40.com.pa/
  • https://los40.com.pa/
226 KB
48 KB
799ms
232ms
Document
text/html
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
655a13e81cc47eb28c0b40b85f014519f3032021817e1579145ca879c9309fcf
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36

Response headers

cache-control
private, max-age=60
content-encoding
gzip
content-length
47982
content-security-policy
upgrade-insecure-requests
content-type
text/html; charset=utf-8
date
Thu, 01 Oct 2026 18:57:05 GMT
etag
W/"38679-HnxksUkFA+7z86O1r5YIWq+KvRM"
expires
Thu, 01 Oct 2026 18:58:05 GMT
last-modified
Thu, 01 Oct 2026 18:56:00 GMT
server
openresty
vary
Accept-Encoding
x-arc-cache-tag
fusion-prisaradiolos40-index-engine-8,fusion-did-prisaradiolos40-index-engine-1025,fusion-pt-prisaradiolos40-index-engine-page,fusion-ptid-prisaradiolos40-index-engine-pvRiEphR4m4QLgnv,fusion-template-id-prisaradiolos40-index-pvRiEphR4m4QLgnv,fusion-cid-prisaradiolos40-index-/los40_panama,url-prisaradiolos40-index-f3c4b076,url-prisaradiolos40-los40-pa-index-f3c4b076
x-arc-edgecontroller
1.8.5
x-arc-pb-edge
0
x-arc-pb-mx-id
00000000
x-arc-pb-request-id
18bce8c7-7210-4da2-a263-71582d81bf10
x-arc-request-id
0.b2163017.1790881024.5f0b
x-arc-ttl
120

Redirect headers

Location
https://los40.com.pa/
Non-Authoritative-Reason
HttpsUpgrades
GET
H2
200
OUGXPMVQPRB3PJUTR5NDNJ6PQA.jpg
los40.com/resizer/v2/
55 KB
55 KB
330ms
225ms
Image
image/avif
2a02:26f0:3500:12::1730:1799
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com/resizer/v2/OUGXPMVQPRB3PJUTR5NDNJ6PQA.jpg?auth=7613b268ae2a71b5f6c43c6e79b401b5127e6c94be49a59b28ba9b1ba6c0720b&quality=70&width=1200&height=675&smart=true
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:1799 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
Akamai Image Manager /
Resource Hash
e621e327dec0160361efd7f426a172ca2bdf6d6c07dc1c4b866357d93ca8f1c6
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests, upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-security-policy
upgrade-insecure-requests, upgrade-insecure-requests
cache-control
private, no-transform, max-age=31328941
x-arc-ttl
31536000
etag
"aaf59b385e29406d2d044e2f0cbb0d95"
expires
Wed, 29 Sep 2027 09:26:06 GMT
content-length
55997
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.99163017.1790881025.184b2588
last-modified
Tue, 29 Sep 2026 09:26:04 GMT
content-type
image/avif
server
Akamai Image Manager
GET
H2
200
outfit.woff2
los40.com.pa/pf/resources/dist/fonts/
34 KB
34 KB
81ms
81ms
Font
font/woff2
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/fonts/outfit.woff2?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
02afbc3f8f6c9db03cb2053aec2dac67d4835891273da81ef6fd34d8949071c4
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

Origin
https://los40.com.pa
sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
x-arc-ttl
31536000
etag
"b3a63e8c6077357264ac7c7cafdfa7b5"
access-control-allow-methods
GET, PUT, POST, HEAD
expires
Fri, 01 Oct 2027 18:57:05 GMT
accept-ranges
bytes
access-control-allow-origin
*, *
content-length
34552
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.5fd7
content-type
font/woff2
last-modified
Thu, 01 Oct 2026 11:11:59 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
nunitoSans-v.woff2
los40.com.pa/pf/resources/dist/fonts/
194 KB
195 KB
28ms
28ms
Font
font/woff2
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/fonts/nunitoSans-v.woff2?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
eb97074105525e11e271010800282a6462ea1c17605019b1a5b09c235ec733bc
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

Origin
https://los40.com.pa
sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
x-arc-ttl
31536000
etag
"81b53a7afa9252433c4edceb86ea48cd"
access-control-allow-methods
GET, PUT, POST, HEAD
expires
Fri, 01 Oct 2027 18:57:05 GMT
accept-ranges
bytes
access-control-allow-origin
*, *
content-length
198924
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.5fd8
content-type
font/woff2
last-modified
Thu, 01 Oct 2026 11:11:59 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
coreplayer_launcher.js Show response
player.prisamedia.com/core/js/
1 KB
884 B
94ms
24ms
Script
application/javascript
199.232.198.133
Fastly
General
Full URL
https://player.prisamedia.com/core/js/coreplayer_launcher.js
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
199.232.198.133 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
/
Resource Hash
3024e387751b683c51e63b3a5b0cbe521795b1dcff0e495cf438211f5205c32d

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
"5222be1202000fdfd45e38d91551e754"
age
22827
x-timer
S1790881025.123361,VS0,VE1
via
1.1 varnish
accept-ranges
bytes
access-control-allow-origin
*
x-cache
HIT
content-length
634
date
Thu, 01 Oct 2026 18:57:05 GMT
last-modified
Thu, 01 Oct 2026 12:36:34 GMT
content-type
application/javascript; charset=utf-8
x-served-by
cache-lin1730051-LIN
x-cache-hits
0
vary
Accept-Encoding
GET
H2
200
cmp.js Show response
cmp.prisa.com/dist/
16 KB
5 KB
90ms
26ms
Script
text/javascript
199.232.198.133
Fastly
General
Full URL
https://cmp.prisa.com/dist/cmp.js
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
199.232.198.133 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
AmazonS3 /
Resource Hash
f81388d87f85f3c9057669770eff0c3b992d135d7eda537d0804a996e178be80

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
"592d1c2292e9c86d4437b6b0e9a4f9f5"
age
50717
x-cache
Miss from cloudfront, HIT
x-amz-cf-id
yHazz3RmeC7u-6kH1Msy0btLCzKQiL-_uSXx1S6N-OVBSvMN-AURvw==
date
Thu, 01 Oct 2026 18:57:05 GMT
content-type
text/javascript
x-served-by
cache-lin1730054-LIN
x-cache-hits
14
last-modified
Tue, 18 Aug 2026 10:17:11 GMT
x-timer
S1790881025.117998,VS0,VE0
via
1.1 fecd699d6b5a3a8d83f9b476d9e7bc1c.cloudfront.net (CloudFront), 1.1 varnish
accept-ranges
bytes
access-control-allow-origin
*
content-length
5137
x-amz-cf-pop
MXP53-P4
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H2
200
pmuser.min.js Show response
static.prisa.com/dist/subs/pmuser/v2/stable/
157 KB
26 KB
90ms
28ms
Script
application/javascript
199.232.198.133
Fastly
General
Full URL
https://static.prisa.com/dist/subs/pmuser/v2/stable/pmuser.min.js
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
199.232.198.133 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
/
Resource Hash
4b8a762bf1f92cafdc2400a4aa5fb13d9dc649999406ecc5c24ec6d28c0994ae

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
"24518ca7b490ab73795e864ee33936d0"
age
68354
x-timer
S1790881025.113764,VS0,VE1
via
1.1 varnish
accept-ranges
bytes
x-cache
HIT
content-length
26168
date
Thu, 01 Oct 2026 18:57:05 GMT
last-modified
Mon, 25 May 2026 07:19:38 GMT
content-type
application/javascript
x-served-by
cache-lin1730060-LIN
x-cache-hits
1
vary
Accept-Encoding,Origin
GET
H2
200
main.js Show response
los40.com.pa/pf/resources/dist/js/
29 KB
10 KB
76ms
74ms
Script
text/javascript
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/js/main.js?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
1056d0181c72eb0d725f840073cbbb5b66a3fdf5926bb70d0ac1096018772ccf
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"b39ffdb024468db48859b54dad708042"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
10114
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.5fe7
content-type
text/javascript; charset=utf-8
last-modified
Thu, 01 Oct 2026 11:12:02 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
lista40.js Show response
los40.com.pa/pf/resources/dist/js/
33 KB
11 KB
120ms
119ms
Script
text/javascript
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/js/lista40.js?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
41971663d4fa9fac35327285ca4844983efbfea78c68335f4885f7d5e8d45aa2
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"d67b6f2fc7acd8b4d379923dc60054f8"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
10851
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.5fe8
content-type
text/javascript; charset=utf-8
last-modified
Thu, 01 Oct 2026 11:12:02 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
seo-bar.js Show response
los40.com.pa/pf/resources/dist/js/
5 KB
2 KB
76ms
75ms
Script
text/javascript
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/js/seo-bar.js?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
6f190eeb69a176008b5f453480c482c64ba9538a0a6b46eefcb0fb3197ad20f4
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"bd71f0d1d7497d3ccd84552c14887359"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
2057
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.5fe9
content-type
text/javascript; charset=utf-8
last-modified
Thu, 01 Oct 2026 11:12:02 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
persistent-player.min.js Show response
los40.com.pa/pf/resources/js/libs/
81 KB
19 KB
77ms
76ms
Script
text/javascript
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/js/libs/persistent-player.min.js?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
42ca9ca6df9f1ce73546272c990ee1475ca10c0032d814e08910c08ba6b990da
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"46aadbe3bcb68b22fa3d2475da5c6201"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
18971
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.5fea
content-type
text/javascript; charset=utf-8
last-modified
Thu, 01 Oct 2026 11:12:06 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
header.min.js Show response
los40.com.pa/pf/resources/js/libs/
4 KB
2 KB
77ms
76ms
Script
text/javascript
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/js/libs/header.min.js?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
ecd9eeb6d9f743ef01d482ca7d9f9b8c49d1fa8d1bd9043a8866d4f476658585
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"156a3dd54e5088677c34367fffa3bfac"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
1568
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.5feb
content-type
text/javascript; charset=utf-8
last-modified
Thu, 01 Oct 2026 11:12:06 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
fRIhCiUVaKs Show response
www.youtube.com/embed/ Frame 8D10
152 KB
64 KB
165ms
109ms
Document
text/html
2001:4860:4826:400::
Google LLC
General
Full URL
https://www.youtube.com/embed/fRIhCiUVaKs
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:4826:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
b4dc09cc9d3cabc8fee6b934540492133215f1ed9bfaf07310316386956cd93d
Security Headers
Name Value
Content-Security-Policy script-src 'unsafe-eval' 'self' 'unsafe-inline' https://www.google.com https://apis.google.com https://ssl.gstatic.com https://www.gstatic.com https://www.googletagmanager.com https://www.google-analytics.com https://*.youtube.com https://*.google.com https://*.gstatic.com https://youtube.com https://www.youtube.com https://google.com https://*.doubleclick.net https://*.googleapis.com https://www.googleadservices.com https://tpc.googlesyndication.com https://www.youtubekids.com https://www.youtube-nocookie.com https://www.youtubeeducation.com https://www-onepick-opensocial.googleusercontent.com;report-uri https://csp.withgoogle.com/csp/youtube_main/allowlist require-trusted-types-for 'script' base-uri 'self';object-src 'none';script-src 'report-sample' 'nonce-fwYMujKO3bX90KY-y90bTw' 'unsafe-inline' 'strict-dynamic' https: http: 'unsafe-eval';report-uri https://csp.withgoogle.com/csp/youtube_main/strict
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://los40.com.pa/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cache-control
no-cache, no-store, max-age=0, must-revalidate
content-encoding
br
content-security-policy
script-src 'unsafe-eval' 'self' 'unsafe-inline' https://www.google.com https://apis.google.com https://ssl.gstatic.com https://www.gstatic.com https://www.googletagmanager.com https://www.google-analytics.com https://*.youtube.com https://*.google.com https://*.gstatic.com https://youtube.com https://www.youtube.com https://google.com https://*.doubleclick.net https://*.googleapis.com https://www.googleadservices.com https://tpc.googlesyndication.com https://www.youtubekids.com https://www.youtube-nocookie.com https://www.youtubeeducation.com https://www-onepick-opensocial.googleusercontent.com;report-uri https://csp.withgoogle.com/csp/youtube_main/allowlist require-trusted-types-for 'script' base-uri 'self';object-src 'none';script-src 'report-sample' 'nonce-fwYMujKO3bX90KY-y90bTw' 'unsafe-inline' 'strict-dynamic' https: http: 'unsafe-eval';report-uri https://csp.withgoogle.com/csp/youtube_main/strict
content-type
text/html; charset=utf-8
cross-origin-embedder-policy-report-only
require-corp; report-to="youtube_main"
cross-origin-opener-policy-report-only
same-origin; report-to="youtube_main"
cross-origin-resource-policy
cross-origin
date
Thu, 01 Oct 2026 18:57:05 GMT
expires
Mon, 01 Jan 1990 00:00:00 GMT
origin-trial
AmhMBR6zCLzDDxpW+HfpP67BqwIknWnyMOXOQGfzYswFmJe+fgaI6XZgAzcxOrzNtP7hEDsOo1jdjFnVr2IdxQ4AAAB4eyJvcmlnaW4iOiJodHRwczovL3lvdXR1YmUuY29tOjQ0MyIsImZlYXR1cmUiOiJXZWJWaWV3WFJlcXVlc3RlZFdpdGhEZXByZWNhdGlvbiIsImV4cGlyeSI6MTc1ODA2NzE5OSwiaXNTdWJkb21haW4iOnRydWV9 AiDEBptUfVeO93q48VdVMe/ubupazdAl8AaHP+NBzdnW8quUcHdzJUyGSfrmtpKJu7EOvwRp9ug2rEo3XU+WMAMAAAB2eyJvcmlnaW4iOiJodHRwczovL3lvdXR1YmUuY29tOjQ0MyIsImZlYXR1cmUiOiJEZXZpY2VCb3VuZFNlc3Npb25DcmVkZW50aWFsczIiLCJleHBpcnkiOjE3NzQzMTA0MDAsImlzU3ViZG9tYWluIjp0cnVlfQ==
p3p
CP="This is not a P3P policy! See http://support.google.com/accounts/answer/151657?hl=de for more info."
permissions-policy
ch-ua-arch=*, ch-ua-bitness=*, ch-ua-full-version=*, ch-ua-full-version-list=*, ch-ua-model=*, ch-ua-wow64=*, ch-ua-form-factors=*, ch-ua-platform=*, ch-ua-platform-version=*
pragma
no-cache
report-to
{"group":"youtube_main","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube_main"}]}
server
ESF
strict-transport-security
max-age=31536000
vary
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
x-content-type-options
nosniff
x-xss-protection
0
GET
H2
200
s3a4OQR-10M Show response
www.youtube.com/embed/ Frame CCE2
151 KB
61 KB
253ms
198ms
Document
text/html
2001:4860:4826:400::
Google LLC
General
Full URL
https://www.youtube.com/embed/s3a4OQR-10M
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:4826:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
c772f5f94c822468df599d6fce72a4b8921390f5fb49b39d7ea6d57492209d7b
Security Headers
Name Value
Content-Security-Policy script-src 'unsafe-eval' 'self' 'unsafe-inline' https://www.google.com https://apis.google.com https://ssl.gstatic.com https://www.gstatic.com https://www.googletagmanager.com https://www.google-analytics.com https://*.youtube.com https://*.google.com https://*.gstatic.com https://youtube.com https://www.youtube.com https://google.com https://*.doubleclick.net https://*.googleapis.com https://www.googleadservices.com https://tpc.googlesyndication.com https://www.youtubekids.com https://www.youtube-nocookie.com https://www.youtubeeducation.com https://www-onepick-opensocial.googleusercontent.com;report-uri https://csp.withgoogle.com/csp/youtube_main/allowlist base-uri 'self';object-src 'none';script-src 'report-sample' 'nonce-uGueggWIV7CQEIJuJFARDQ' 'unsafe-inline' 'strict-dynamic' https: http: 'unsafe-eval';report-uri https://csp.withgoogle.com/csp/youtube_main/strict require-trusted-types-for 'script'
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://los40.com.pa/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cache-control
no-cache, no-store, max-age=0, must-revalidate
content-encoding
br
content-security-policy
script-src 'unsafe-eval' 'self' 'unsafe-inline' https://www.google.com https://apis.google.com https://ssl.gstatic.com https://www.gstatic.com https://www.googletagmanager.com https://www.google-analytics.com https://*.youtube.com https://*.google.com https://*.gstatic.com https://youtube.com https://www.youtube.com https://google.com https://*.doubleclick.net https://*.googleapis.com https://www.googleadservices.com https://tpc.googlesyndication.com https://www.youtubekids.com https://www.youtube-nocookie.com https://www.youtubeeducation.com https://www-onepick-opensocial.googleusercontent.com;report-uri https://csp.withgoogle.com/csp/youtube_main/allowlist base-uri 'self';object-src 'none';script-src 'report-sample' 'nonce-uGueggWIV7CQEIJuJFARDQ' 'unsafe-inline' 'strict-dynamic' https: http: 'unsafe-eval';report-uri https://csp.withgoogle.com/csp/youtube_main/strict require-trusted-types-for 'script'
content-type
text/html; charset=utf-8
cross-origin-embedder-policy-report-only
require-corp; report-to="youtube_main"
cross-origin-opener-policy-report-only
same-origin; report-to="youtube_main"
cross-origin-resource-policy
cross-origin
date
Thu, 01 Oct 2026 18:57:05 GMT
expires
Mon, 01 Jan 1990 00:00:00 GMT
origin-trial
AmhMBR6zCLzDDxpW+HfpP67BqwIknWnyMOXOQGfzYswFmJe+fgaI6XZgAzcxOrzNtP7hEDsOo1jdjFnVr2IdxQ4AAAB4eyJvcmlnaW4iOiJodHRwczovL3lvdXR1YmUuY29tOjQ0MyIsImZlYXR1cmUiOiJXZWJWaWV3WFJlcXVlc3RlZFdpdGhEZXByZWNhdGlvbiIsImV4cGlyeSI6MTc1ODA2NzE5OSwiaXNTdWJkb21haW4iOnRydWV9 AiDEBptUfVeO93q48VdVMe/ubupazdAl8AaHP+NBzdnW8quUcHdzJUyGSfrmtpKJu7EOvwRp9ug2rEo3XU+WMAMAAAB2eyJvcmlnaW4iOiJodHRwczovL3lvdXR1YmUuY29tOjQ0MyIsImZlYXR1cmUiOiJEZXZpY2VCb3VuZFNlc3Npb25DcmVkZW50aWFsczIiLCJleHBpcnkiOjE3NzQzMTA0MDAsImlzU3ViZG9tYWluIjp0cnVlfQ==
p3p
CP="This is not a P3P policy! See http://support.google.com/accounts/answer/151657?hl=de for more info."
permissions-policy
ch-ua-arch=*, ch-ua-bitness=*, ch-ua-full-version=*, ch-ua-full-version-list=*, ch-ua-model=*, ch-ua-wow64=*, ch-ua-form-factors=*, ch-ua-platform=*, ch-ua-platform-version=*
pragma
no-cache
report-to
{"group":"youtube_main","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube_main"}]}
server
ESF
strict-transport-security
max-age=31536000
vary
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
x-content-type-options
nosniff
x-xss-protection
0
GET
H2
200
_1W51TfwOEA Show response
www.youtube.com/embed/ Frame B420
152 KB
61 KB
192ms
137ms
Document
text/html
2001:4860:4826:400::
Google LLC
General
Full URL
https://www.youtube.com/embed/_1W51TfwOEA
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:4826:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
038e94abcde149f32572693ff5883e880c4f08a63df56f27ea8eeefdb329a753
Security Headers
Name Value
Content-Security-Policy script-src 'unsafe-eval' 'self' 'unsafe-inline' https://www.google.com https://apis.google.com https://ssl.gstatic.com https://www.gstatic.com https://www.googletagmanager.com https://www.google-analytics.com https://*.youtube.com https://*.google.com https://*.gstatic.com https://youtube.com https://www.youtube.com https://google.com https://*.doubleclick.net https://*.googleapis.com https://www.googleadservices.com https://tpc.googlesyndication.com https://www.youtubekids.com https://www.youtube-nocookie.com https://www.youtubeeducation.com https://www-onepick-opensocial.googleusercontent.com;report-uri https://csp.withgoogle.com/csp/youtube_main/allowlist require-trusted-types-for 'script' base-uri 'self';object-src 'none';script-src 'report-sample' 'nonce-G0YQE-Nnkw84woauRV5Z7Q' 'unsafe-inline' 'strict-dynamic' https: http: 'unsafe-eval';report-uri https://csp.withgoogle.com/csp/youtube_main/strict
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://los40.com.pa/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cache-control
no-cache, no-store, max-age=0, must-revalidate
content-encoding
br
content-security-policy
script-src 'unsafe-eval' 'self' 'unsafe-inline' https://www.google.com https://apis.google.com https://ssl.gstatic.com https://www.gstatic.com https://www.googletagmanager.com https://www.google-analytics.com https://*.youtube.com https://*.google.com https://*.gstatic.com https://youtube.com https://www.youtube.com https://google.com https://*.doubleclick.net https://*.googleapis.com https://www.googleadservices.com https://tpc.googlesyndication.com https://www.youtubekids.com https://www.youtube-nocookie.com https://www.youtubeeducation.com https://www-onepick-opensocial.googleusercontent.com;report-uri https://csp.withgoogle.com/csp/youtube_main/allowlist require-trusted-types-for 'script' base-uri 'self';object-src 'none';script-src 'report-sample' 'nonce-G0YQE-Nnkw84woauRV5Z7Q' 'unsafe-inline' 'strict-dynamic' https: http: 'unsafe-eval';report-uri https://csp.withgoogle.com/csp/youtube_main/strict
content-type
text/html; charset=utf-8
cross-origin-embedder-policy-report-only
require-corp; report-to="youtube_main"
cross-origin-opener-policy-report-only
same-origin; report-to="youtube_main"
cross-origin-resource-policy
cross-origin
date
Thu, 01 Oct 2026 18:57:05 GMT
expires
Mon, 01 Jan 1990 00:00:00 GMT
origin-trial
AmhMBR6zCLzDDxpW+HfpP67BqwIknWnyMOXOQGfzYswFmJe+fgaI6XZgAzcxOrzNtP7hEDsOo1jdjFnVr2IdxQ4AAAB4eyJvcmlnaW4iOiJodHRwczovL3lvdXR1YmUuY29tOjQ0MyIsImZlYXR1cmUiOiJXZWJWaWV3WFJlcXVlc3RlZFdpdGhEZXByZWNhdGlvbiIsImV4cGlyeSI6MTc1ODA2NzE5OSwiaXNTdWJkb21haW4iOnRydWV9 AiDEBptUfVeO93q48VdVMe/ubupazdAl8AaHP+NBzdnW8quUcHdzJUyGSfrmtpKJu7EOvwRp9ug2rEo3XU+WMAMAAAB2eyJvcmlnaW4iOiJodHRwczovL3lvdXR1YmUuY29tOjQ0MyIsImZlYXR1cmUiOiJEZXZpY2VCb3VuZFNlc3Npb25DcmVkZW50aWFsczIiLCJleHBpcnkiOjE3NzQzMTA0MDAsImlzU3ViZG9tYWluIjp0cnVlfQ==
p3p
CP="This is not a P3P policy! See http://support.google.com/accounts/answer/151657?hl=de for more info."
permissions-policy
ch-ua-arch=*, ch-ua-bitness=*, ch-ua-full-version=*, ch-ua-full-version-list=*, ch-ua-model=*, ch-ua-wow64=*, ch-ua-form-factors=*, ch-ua-platform=*, ch-ua-platform-version=*
pragma
no-cache
report-to
{"group":"youtube_main","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube_main"}]}
server
ESF
strict-transport-security
max-age=31536000
vary
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
x-content-type-options
nosniff
x-xss-protection
0
GET
H2
200
l-los40.svg
los40.com.pa/pf/resources/dist/img/
41 KB
29 KB
78ms
76ms
Image
image/svg+xml
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/img/l-los40.svg?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
5228e2d37779820e50e291ac069ec397f6712df232452640a9210a6fd91a9cc7
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"c5a9311a3eb05320fad738826cb36491"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
29627
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.5fec
content-type
image/svg+xml
last-modified
Thu, 01 Oct 2026 11:12:01 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
map-esp.svg
los40.com.pa/pf/resources/dist/img/
299 KB
37 KB
136ms
134ms
Image
image/svg+xml
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/img/map-esp.svg?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
a55ed8ebc054d8632fd0afb1b06f43c47f5b4d18842303fb109076aecefbd03f
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"584628808a12f95a22066b8e90e2a3f8"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
37634
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.5ff0
content-type
image/svg+xml
last-modified
Thu, 01 Oct 2026 11:12:02 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
ico-fl-ab-cl6.svg
los40.com.pa/pf/resources/dist/img/
1 KB
953 B
88ms
86ms
Image
image/svg+xml
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/img/ico-fl-ab-cl6.svg?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
1b2755ef1cd36503c1c9b048ddf83eda7feb1bbf691bb26f277029f6a876f896
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"af7755c3dcb61feeeac50aa084f1f536"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
636
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.5ff1
content-type
image/svg+xml
last-modified
Thu, 01 Oct 2026 11:12:00 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
ico-play-cl9.svg
los40.com.pa/pf/resources/dist/img/
736 B
766 B
85ms
83ms
Image
image/svg+xml
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/img/ico-play-cl9.svg?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
d37b5f9b60958395c3cab7207c76ed40d7fc4d9b6efe9f942f7461500cf9cccf
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"d10c8a9bde3673c00a9f88d21a0c7662"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
449
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.5ff2
content-type
image/svg+xml
last-modified
Thu, 01 Oct 2026 11:12:01 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
ico-fl-ar.svg
los40.com.pa/pf/resources/dist/img/
1 KB
1023 B
88ms
85ms
Image
image/svg+xml
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/img/ico-fl-ar.svg?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
622131b4cece767db3c86041482e1103b5b90ed911333d08e04c6c4af55c4da3
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"013c029f937e0c4048c3626460e2feda"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
706
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.5ff3
content-type
image/svg+xml
last-modified
Thu, 01 Oct 2026 11:12:00 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
ico-app-cl24.svg
los40.com.pa/pf/resources/dist/img/
2 KB
967 B
85ms
83ms
Image
image/svg+xml
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/img/ico-app-cl24.svg?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
29dafeba1ea69519e201f76e76ba1a7fb508554c443e33792ea4e48a4369e5e2
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"0814e944a667f3e2e2b67c8133bb3ac3"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
650
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.5ff4
content-type
image/svg+xml
last-modified
Thu, 01 Oct 2026 11:11:59 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
ico-fb-cl22.svg
los40.com.pa/pf/resources/dist/img/
968 B
809 B
87ms
85ms
Image
image/svg+xml
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/img/ico-fb-cl22.svg?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
ba6730bccf913770e4062dfa49fab7fff5320146296a9d34a8795ea74c579551
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"593268b8d7fa2c5ae9a777f18bcb3283"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
492
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.5ff5
content-type
image/svg+xml
last-modified
Thu, 01 Oct 2026 11:12:00 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
ico-tw-cl22.svg
los40.com.pa/pf/resources/dist/img/
758 B
766 B
84ms
82ms
Image
image/svg+xml
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/img/ico-tw-cl22.svg?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
769b47f6cb38895551a44b064e4afd8f7e13bb9ec15bda07443cfcd10e20c150
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"0ef6b47a08a2f25615c48fe3026e98db"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
449
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.5ff6
content-type
image/svg+xml
last-modified
Thu, 01 Oct 2026 11:12:01 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
ico-ig-cl1.svg
los40.com.pa/pf/resources/dist/img/
3 KB
1 KB
83ms
81ms
Image
image/svg+xml
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/img/ico-ig-cl1.svg?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
8976b88cd7b0fac9110721d5ee1e0471111cf8b313616541a5a1bf7b773742f3
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"c14e01e2674ca5edee85b6477c3f9ba3"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
1136
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.5ff7
content-type
image/svg+xml
last-modified
Thu, 01 Oct 2026 11:12:00 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
ico-l-igu.svg
los40.com.pa/pf/resources/dist/img/
1 KB
861 B
84ms
82ms
Image
image/svg+xml
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/img/ico-l-igu.svg?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
501cda4917af84bbaf002d6b53d606403fe7a2a5549a596d680249f9d8cc10bc
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"83e94cd6374adbdc7c42d817ead7e137"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
544
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.5ff8
content-type
image/svg+xml
last-modified
Thu, 01 Oct 2026 11:12:00 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
ico-l-up.svg
los40.com.pa/pf/resources/dist/img/
2 KB
1 KB
84ms
82ms
Image
image/svg+xml
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/img/ico-l-up.svg?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
09d4ace821999277a3db65e31a074ae22b628dd21100cdb4a37127a8e291631b
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"281c3d1b3fee2b8697f5d7a600c1965b"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
800
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.5ff9
content-type
image/svg+xml
last-modified
Thu, 01 Oct 2026 11:12:00 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
ico-l-dwn.svg
los40.com.pa/pf/resources/dist/img/
2 KB
1 KB
84ms
82ms
Image
image/svg+xml
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/img/ico-l-dwn.svg?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
d4f23126c68b19daf5da6627ce56905644a3cc06f634a576428cf7095e923d26
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"1ee1624c9aecfe5c2dbd3bbe61d637db"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
743
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.5ffa
content-type
image/svg+xml
last-modified
Thu, 01 Oct 2026 11:12:00 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
ico-fb-cr-cl4.svg
los40.com.pa/pf/resources/dist/img/
1 KB
893 B
84ms
83ms
Image
image/svg+xml
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/img/ico-fb-cr-cl4.svg?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
20d31559e45ce5462a4dd4e20410e48dc28798967f7bced6740439e5a350ee3f
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"4ee07f8e334b1749da65b7beabbbeb79"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
576
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.5ffb
content-type
image/svg+xml
last-modified
Thu, 01 Oct 2026 11:12:00 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
ico-tw-cr-cl4.svg
los40.com.pa/pf/resources/dist/img/
842 B
746 B
87ms
86ms
Image
image/svg+xml
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/img/ico-tw-cr-cl4.svg?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
6c84b666d4df1743ad060633775e7d7caf97c85fb28a84f55a9c3eeb6e090b5e
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"eb0a535f56df6846d6c467a2672e1252"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
429
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.5ffc
content-type
image/svg+xml
last-modified
Thu, 01 Oct 2026 11:12:01 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
ico-ig-cr-cl4.svg
los40.com.pa/pf/resources/dist/img/
4 KB
2 KB
86ms
84ms
Image
image/svg+xml
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/img/ico-ig-cr-cl4.svg?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
2755d9f1441bb50077d6db548a0a9188f095b12619741e5db452e9c02beebcd4
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"a6a67d331ee362e76c4cc644503d1c8a"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
1844
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.5ffd
content-type
image/svg+xml
last-modified
Thu, 01 Oct 2026 11:12:00 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
https%3A%2F%2Fwww.prisacom.com%2Fcomunes%2Fpiecomun-v9%2Fimgs%2Fpiev9-2013_light.png%3Fv2
los40.com/resizer/v2/
13 KB
14 KB
412ms
321ms
Image
image/avif
2a02:26f0:3500:12::1730:1799
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com/resizer/v2/https%3A%2F%2Fwww.prisacom.com%2Fcomunes%2Fpiecomun-v9%2Fimgs%2Fpiev9-2013_light.png%3Fv2?auth=01ab017f1c26f930e70ebc45366f3c4d619d5b59f45d665a20f63d05aeb60b42&quality=70
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:1799 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
Akamai Image Manager /
Resource Hash
c6a6b60c1bcd1083c32e2d1809b4d91a699d6072aa42e612626ecc8977757aa5
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests, upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-security-policy
upgrade-insecure-requests, upgrade-insecure-requests
cache-control
private, no-transform, max-age=31464619
x-arc-ttl
31536000
etag
"9aa8b61a0bfa3b1b04d8d9ab2f9dcb12"
expires
Thu, 30 Sep 2027 23:07:24 GMT
content-length
13529
x-serial
1901
date
Thu, 01 Oct 2026 18:57:05 GMT
last-modified
Wed, 30 Sep 2026 23:07:24 GMT
content-type
image/avif
server
Akamai Image Manager
x-arc-request-id
0.99163017.1790881025.184b2589
GET
H2
200
ico-prev-cl4.svg
los40.com.pa/pf/resources/dist/img/
1 KB
905 B
87ms
85ms
Image
image/svg+xml
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/img/ico-prev-cl4.svg?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
60486887aff825b8083b9f9bbd60a7c994bee63e7de6775bd2afd596e6fe3e97
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"086db56907327580bcdf631724ac0c51"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
588
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.5ffe
content-type
image/svg+xml
last-modified
Thu, 01 Oct 2026 11:12:01 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
ico-prev-15-cl4.svg
los40.com.pa/pf/resources/dist/img/
1 KB
942 B
82ms
81ms
Image
image/svg+xml
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/img/ico-prev-15-cl4.svg?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
966aa4cc84973eff8c83b4013c6e58dd9bfe06a2e8ad88b68e5c938c84fde4ff
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"241056adccd0e9db3d7ed4f359a3d317"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
625
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.5fff
content-type
image/svg+xml
last-modified
Thu, 01 Oct 2026 11:12:01 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
ico-forw-15-cl4.svg
los40.com.pa/pf/resources/dist/img/
1 KB
945 B
87ms
86ms
Image
image/svg+xml
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/img/ico-forw-15-cl4.svg?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
89dec1f10ed0da63883beaa22f8476b4ace5a0709a7a5cdea8fcb3d6bb38172e
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"ae1e489e406cdf11d704534997bf9bed"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
629
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.6000
content-type
image/svg+xml
last-modified
Thu, 01 Oct 2026 11:12:00 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
ico-forw-cl4.svg
los40.com.pa/pf/resources/dist/img/
969 B
863 B
87ms
86ms
Image
image/svg+xml
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/img/ico-forw-cl4.svg?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
db37415538fa6f3279331fc6ae11a7839a953e6aed04717013658ede7ad224e3
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"49abbebb11bf937f5063135bee6a5d77"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
547
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.6001
content-type
image/svg+xml
last-modified
Thu, 01 Oct 2026 11:12:00 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
ico-fl-bold-ar.svg
los40.com.pa/pf/resources/dist/img/
270 B
523 B
86ms
85ms
Image
image/svg+xml
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/img/ico-fl-bold-ar.svg?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
68f1b808fa4dc0c3104b1dc2bffadc6517167840a3b0f9dd9ac0011d4cec0cec
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"3d215fc587e8b461c317f1d114fae108"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
208
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.6002
content-type
image/svg+xml
last-modified
Thu, 01 Oct 2026 11:12:00 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
ico-cl.svg
los40.com.pa/pf/resources/dist/img/
1 KB
976 B
85ms
85ms
Image
image/svg+xml
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/img/ico-cl.svg?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
53bea1615bdbda079c26a285ec2c2c96fdcfd2fc6d6eb22a435ac9278a967a8b
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"b16f1047b63f65ab2f75ffa5a905c0f6"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
660
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.6003
content-type
image/svg+xml
last-modified
Thu, 01 Oct 2026 11:12:00 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
ico-sha.svg
los40.com.pa/pf/resources/dist/img/
2 KB
1 KB
86ms
85ms
Image
image/svg+xml
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/img/ico-sha.svg?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
3718414c79ddd99304d70bf93704327a8b20b02fa45bf36a907fea538830555e
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"a289dab6e187fc01bde805453d944a7d"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
949
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.6004
content-type
image/svg+xml
last-modified
Thu, 01 Oct 2026 11:12:01 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
ico-vol.svg
los40.com.pa/pf/resources/dist/img/
3 KB
2 KB
86ms
86ms
Image
image/svg+xml
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/img/ico-vol.svg?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
e5920add0f05bf998d8605cbd92fe34a5aaf0bad21d312a67cbf10288442e7b2
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"488ae957507510e61676e83078f3e1c2"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
1325
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.6005
content-type
image/svg+xml
last-modified
Thu, 01 Oct 2026 11:12:01 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
DO76KFXQK5BC7I2QJROZUERUDY.jpg
los40.com/resizer/v2/
10 KB
10 KB
294ms
286ms
Image
image/avif
2a02:26f0:3500:12::1730:1799
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com/resizer/v2/DO76KFXQK5BC7I2QJROZUERUDY.jpg?auth=6f4950a3812dd3dabfe5c29350c2172e1d9ba2a51be2263dc03a8cf42db4ec13&quality=70&width=778&height=437&smart=true
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:1799 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
Akamai Image Manager /
Resource Hash
70a06dcb720f594a598a01fcfdd7769a1178076f803d61d3da7efab4384f5141
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests, upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

mpulse_cdn_cache
HIT
content-security-policy
upgrade-insecure-requests, upgrade-insecure-requests
cache-control
private, no-transform, max-age=31249272
x-arc-ttl
31536000
etag
"c8835f129e77d7acdff00cb7cd76e6aa"
mpulse_origin_time
0
x-edgeconnect-cache-status
1
expires
Tue, 28 Sep 2027 11:18:17 GMT
content-length
10277
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.99163017.1790881025.184b25c4
last-modified
Mon, 28 Sep 2026 11:18:16 GMT
content-type
image/avif
server
Akamai Image Manager
GET
H2
200
3QFPRIFV3ZFMZH4NR5H3G2G5LQ.jpg
los40.com/resizer/v2/
12 KB
13 KB
377ms
370ms
Image
image/avif
2a02:26f0:3500:12::1730:1799
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com/resizer/v2/3QFPRIFV3ZFMZH4NR5H3G2G5LQ.jpg?auth=006009f88f25c03049feccc3d8bf4335391caa9070608f8175d15fd680fbe139&quality=70&width=778&height=437&smart=true
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:1799 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
Akamai Image Manager /
Resource Hash
c1cb67546b0fedd9ece25b45e7ada8ee0f85d6c02a35865139f4bddfa3eca6d2
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests, upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

mpulse_cdn_cache
HIT
content-security-policy
upgrade-insecure-requests, upgrade-insecure-requests
cache-control
private, no-transform, max-age=31340007
x-arc-ttl
31536000
etag
"28a4cc22757014bcb6632cc29cb5c23d"
mpulse_origin_time
0
expires
Wed, 29 Sep 2027 12:30:32 GMT
content-length
12795
x-serial
639
date
Thu, 01 Oct 2026 18:57:05 GMT
last-modified
Tue, 29 Sep 2026 12:30:31 GMT
content-type
image/avif
server
Akamai Image Manager
x-arc-request-id
0.99163017.1790881025.184b25c2
GET
H2
200
ICCHMUNE2FAGXFJ4SE2UUNDG3Q.jpg
los40.com/resizer/v2/
59 KB
60 KB
328ms
321ms
Image
image/avif
2a02:26f0:3500:12::1730:1799
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com/resizer/v2/ICCHMUNE2FAGXFJ4SE2UUNDG3Q.jpg?auth=197f9725d4bc11696c8e8fc8040806a3949f3aa4b5cc7b85bcb2dd9348cce9be&quality=70&width=1200&height=675&focal=868,218
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:1799 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
Akamai Image Manager /
Resource Hash
c1935ffb200277c95a9eca8348b29f1c7dbf0e2b548ab9fb6585f259b0b89bb6
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests, upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-security-policy
upgrade-insecure-requests, upgrade-insecure-requests
cache-control
private, no-transform, max-age=31249708
x-arc-ttl
31536000
etag
"02913c2d6374e969b354820775c93f7c"
expires
Tue, 28 Sep 2027 11:25:33 GMT
content-length
60655
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.99163017.1790881025.184b25c3
last-modified
Mon, 28 Sep 2026 11:25:32 GMT
content-type
image/avif
server
Akamai Image Manager
GET
H2
200
6SJRM6YQUJBLJORTVFQQDSM3EE.jpg
los40.com/resizer/v2/
4 KB
4 KB
337ms
330ms
Image
image/avif
2a02:26f0:3500:12::1730:1799
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com/resizer/v2/6SJRM6YQUJBLJORTVFQQDSM3EE.jpg?auth=1569d4080dcb698320f37e3d7d6033030ddcf49419b4e12768b0d5dbcf2204d7&quality=70&width=778&height=437&focal=630,503
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:1799 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
Akamai Image Manager /
Resource Hash
b4f1713861ee9b24b143a5bc92172c5aaf9af76e8406593516551177d0843d5f
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests, upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-security-policy
upgrade-insecure-requests, upgrade-insecure-requests
cache-control
private, no-transform, max-age=31340561
x-arc-ttl
31536000
etag
"85c03f64780198bb1478b1bb02f854c0"
x-edgeconnect-cache-status
1
expires
Wed, 29 Sep 2027 12:39:46 GMT
content-length
4179
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.99163017.1790881025.184b258a
last-modified
Tue, 29 Sep 2026 12:39:46 GMT
content-type
image/avif
server
Akamai Image Manager
GET
H2
200
https%3A%2F%2Frecursosweb.prisaradio.com%2Ffotos%2Fdest%2F490006502356.jpg
los40.com/resizer/v2/
3 KB
3 KB
240ms
238ms
Image
image/avif
2a02:26f0:3500:12::1730:1799
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com/resizer/v2/https%3A%2F%2Frecursosweb.prisaradio.com%2Ffotos%2Fdest%2F490006502356.jpg?auth=c09f06fbfcfef2f03da56f9cdb931cc14cd4a5182e7ae23d2e328c2053b96a76
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:1799 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
Akamai Image Manager /
Resource Hash
8a3eb03ff1cddcb8cf9bedf5b93c288e515bb55c5df8add5e283efb2d7099851
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests, upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

mpulse_cdn_cache
HIT
content-security-policy
upgrade-insecure-requests, upgrade-insecure-requests
cache-control
private, no-transform, max-age=30916964
x-arc-ttl
31536000
etag
"f47bb580a365a941ed2f6683e409870f"
mpulse_origin_time
0
expires
Fri, 24 Sep 2027 14:59:49 GMT
access-control-allow-origin
*
content-length
2655
x-serial
602
date
Thu, 01 Oct 2026 18:57:05 GMT
last-modified
Thu, 24 Sep 2026 14:59:49 GMT
content-type
image/avif
server
Akamai Image Manager
x-arc-request-id
0.99163017.1790881025.184b25c5
GET
H2
200
https%3A%2F%2Fcadenaser00.epimg.net%2Festaticos%2Frecursosgraficos%2Fprueba%2Flos40Global%2Fimg%2Flstn-apl.png
los40.com/resizer/v2/
2 KB
2 KB
250ms
249ms
Image
image/avif
2a02:26f0:3500:12::1730:1799
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com/resizer/v2/https%3A%2F%2Fcadenaser00.epimg.net%2Festaticos%2Frecursosgraficos%2Fprueba%2Flos40Global%2Fimg%2Flstn-apl.png?auth=4a2912f89f3d3cd37f9194cc6b81c5d456130233e56a1329b046254d82e8d089&quality=70&width=212&height=62&smart=true
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:1799 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
Akamai Image Manager /
Resource Hash
f5c302502fb11d97d13043e834e5c2b934bb54b61d0989685c2dc27287452e96
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests, upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-security-policy
upgrade-insecure-requests, upgrade-insecure-requests
cache-control
private, no-transform, max-age=30893631
x-arc-ttl
31536000
etag
"65116de0-1ca4"
expires
Fri, 24 Sep 2027 08:30:56 GMT
content-length
2194
x-serial
1486
date
Thu, 01 Oct 2026 18:57:05 GMT
last-modified
Thu, 24 Sep 2026 08:30:55 GMT
content-type
image/avif
server
Akamai Image Manager
x-arc-request-id
0.99163017.1790881025.184b25c6
GET
H2
200
https%3A%2F%2Frecursosweb.prisaradio.com%2Ffotos%2Fdest%2F490006480815.jpg
los40.com/resizer/v2/
6 KB
6 KB
250ms
249ms
Image
image/avif
2a02:26f0:3500:12::1730:1799
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com/resizer/v2/https%3A%2F%2Frecursosweb.prisaradio.com%2Ffotos%2Fdest%2F490006480815.jpg?auth=307b3fc7258dd5caa7f1a03bda077514f03a3ed1f09af3765b5a16893ab8e889
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:1799 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
Akamai Image Manager /
Resource Hash
3053e145611a5994e86254654465ab2692aaedb3af72ffa04452aa39ffdbc799
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests, upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-security-policy
upgrade-insecure-requests, upgrade-insecure-requests
cache-control
private, no-transform, max-age=31415848
x-arc-ttl
31536000
etag
"c9940e17ca0002670fecfebade1feefe"
expires
Thu, 30 Sep 2027 09:34:33 GMT
access-control-allow-origin
*
content-length
5757
x-serial
1262
date
Thu, 01 Oct 2026 18:57:05 GMT
last-modified
Wed, 30 Sep 2026 09:34:32 GMT
content-type
image/avif
server
Akamai Image Manager
x-arc-request-id
0.99163017.1790881025.184b25c7
GET
H2
200
https%3A%2F%2Frecursosweb.prisaradio.com%2Ffotos%2Fdest%2F010006383479.jpg
los40.com/resizer/v2/
4 KB
4 KB
252ms
251ms
Image
image/avif
2a02:26f0:3500:12::1730:1799
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com/resizer/v2/https%3A%2F%2Frecursosweb.prisaradio.com%2Ffotos%2Fdest%2F010006383479.jpg?auth=c955597c8633d51ecd7edbf090fdd42b4f095e3f21a86676a50e3de93b055c90
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:1799 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
Akamai Image Manager /
Resource Hash
00df653296a4836407e88e03794a222fd8701a823752c35f025ca4fabf7b4b48
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests, upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

mpulse_cdn_cache
MISS
content-security-policy
upgrade-insecure-requests, upgrade-insecure-requests
cache-control
private, no-transform, max-age=31415847
x-arc-ttl
31536000
etag
"d2cc4ea1cfe994471e3fabc5f69443c7"
mpulse_origin_time
40
expires
Thu, 30 Sep 2027 09:34:32 GMT
access-control-allow-origin
*
content-length
3957
x-serial
416
date
Thu, 01 Oct 2026 18:57:05 GMT
last-modified
Wed, 30 Sep 2026 09:34:32 GMT
content-type
image/avif
server
Akamai Image Manager
x-arc-request-id
0.99163017.1790881025.184b25c8
GET
H2
200
https%3A%2F%2Frecursosweb.prisaradio.com%2Ffotos%2Fdest%2F490006479685.jpg
los40.com/resizer/v2/
2 KB
2 KB
253ms
251ms
Image
image/avif
2a02:26f0:3500:12::1730:1799
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com/resizer/v2/https%3A%2F%2Frecursosweb.prisaradio.com%2Ffotos%2Fdest%2F490006479685.jpg?auth=2450790cfb5989e3d931e82d80b8f43b16ae2d28478584dc249fcb0cf3867f7c
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:1799 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
Akamai Image Manager /
Resource Hash
73636f1d6c2d28f48d82ddc0c4a77d397a6acc9ed2b7b014d03f717c4c3e406e
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests, upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

mpulse_cdn_cache
MISS
content-security-policy
upgrade-insecure-requests, upgrade-insecure-requests
cache-control
private, no-transform, max-age=31415849
x-arc-ttl
31536000
etag
"5172d827aa6bcfe048858ae46564870e"
mpulse_origin_time
76
expires
Thu, 30 Sep 2027 09:34:34 GMT
access-control-allow-origin
*
content-length
1835
x-serial
382
date
Thu, 01 Oct 2026 18:57:05 GMT
last-modified
Wed, 30 Sep 2026 09:34:34 GMT
content-type
image/avif
server
Akamai Image Manager
x-arc-request-id
0.99163017.1790881025.184b25c9
GET
H2
200
DJTR3UOHJVGVHIYW27AZOXFCPI.jpg
los40.com/resizer/v2/
10 KB
10 KB
368ms
367ms
Image
image/avif
2a02:26f0:3500:12::1730:1799
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com/resizer/v2/DJTR3UOHJVGVHIYW27AZOXFCPI.jpg?auth=2b4a8862b56efa4404f798ca48ba37bfed3d057793d2a396eb20ac70697c46b7&quality=70&width=778&height=437&smart=true
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:1799 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
Akamai Image Manager /
Resource Hash
f1451e046925e9b7adad6c742d5c9c7e1bcdacb9387dbe4869615f8b93e83cf1
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests, upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-security-policy
upgrade-insecure-requests, upgrade-insecure-requests
cache-control
private, no-transform, max-age=31340562
x-arc-ttl
31536000
etag
"fd2bdc7cbe6962ca4447c57450818a05"
expires
Wed, 29 Sep 2027 12:39:47 GMT
content-length
10176
x-serial
1785
date
Thu, 01 Oct 2026 18:57:05 GMT
last-modified
Tue, 29 Sep 2026 12:39:45 GMT
content-type
image/avif
server
Akamai Image Manager
x-arc-request-id
0.99163017.1790881025.184b25ca
GET
H2
200
bundle_all.css
los40.com.pa/pf/resources/dist/css/los40-pa/
300 KB
51 KB
29ms
29ms
Stylesheet
text/css
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/css/los40-pa/bundle_all.css?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
8494b27686c18de5dc85774c56197edd88739bdbf11535b591323749af7aca80
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"2215546340d8353001e3b887bc321ca8"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
51784
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.605b
content-type
text/css; charset=utf-8
last-modified
Thu, 01 Oct 2026 11:11:58 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
bundle_all_print.css
los40.com.pa/pf/resources/dist/css/los40-pa/
308 KB
52 KB
32ms
31ms
Stylesheet
text/css
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/css/los40-pa/bundle_all_print.css?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
b27c23322be7fc48ca63848b2024c7910a462a6702d9f54fe921f50a5f161422
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"aa1869f8801ec84f42d527627747b4d9"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
53034
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.605c
content-type
text/css; charset=utf-8
last-modified
Thu, 01 Oct 2026 11:11:58 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
coreplayer.min.js Show response
player.prisamedia.com/core//js/
299 KB
74 KB
21ms
21ms
Script
application/javascript
199.232.198.133
Fastly
General
Full URL
https://player.prisamedia.com/core//js/coreplayer.min.js
Requested by
Host: player.prisamedia.com
URL: https://player.prisamedia.com/core/js/coreplayer_launcher.js
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
199.232.198.133 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
/
Resource Hash
91f11824da56ff57eb156e208f66929898d919f9fcc60789a4670cf9755db30d

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
"d5cd046a21bbbe09a907bca4e55b5985"
age
22827
x-timer
S1790881025.155789,VS0,VE0
via
1.1 varnish
accept-ranges
bytes
access-control-allow-origin
*
x-cache
HIT
content-length
75232
date
Thu, 01 Oct 2026 18:57:05 GMT
last-modified
Thu, 01 Oct 2026 12:36:34 GMT
content-type
application/javascript; charset=utf-8
x-served-by
cache-lin1730051-LIN
x-cache-hits
99
vary
Accept-Encoding
GET
H2
200
loader.js Show response
sdk.privacy-center.org/8ba38674-edba-484d-8053-435051d79f72/
116 KB
32 KB
176ms
113ms
Script
application/javascript
2600:9000:28eb:1000:5:b7cc:d3c0:93a1
Amazon.com
General
Full URL
https://sdk.privacy-center.org/8ba38674-edba-484d-8053-435051d79f72/loader.js?target=los40.com.pa
Requested by
Host: cmp.prisa.com
URL: https://cmp.prisa.com/dist/cmp.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2600:9000:28eb:1000:5:b7cc:d3c0:93a1 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
Software
/
Resource Hash
3598ed32f0f6fec1accc27e8d084f15cf77a451ddf649cae9be98b0da1d8b0f4

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=7200, public
x-didomi-remote-config-metadata
multiReg:true;legacyGlobalGdpr:false
content-encoding
br
etag
W/"8a80da0981e13c558b6959006009e069"
x-amzn-trace-id
Root=1-6abead01-087f84a57b39f7ac2ed36e4b;Parent=1c7ed8b522024f92;Sampled=0;Lineage=1:eaae1266:0
x-amzn-requestid
2b33dbab-05e1-4eb7-be0d-1584b063537f
via
1.1 90a1c9bfae56eb9062f3a496d1877f0c.cloudfront.net (CloudFront)
x-didomi-configs-version
173
alt-svc
h3=":443"; ma=86400
x-cache
Miss from cloudfront
x-amz-cf-id
8YM9jyn3rcAmMvWjeo2MC0NJN7VUIv-dCUEe5qtWKQ0zy4CvuEX75w==
date
Thu, 01 Oct 2026 18:57:05 GMT
content-type
application/javascript; charset=utf-8
vary
Accept-Encoding
x-amz-cf-pop
FRA60-P12
GET
H2
200
launch-4756de8c2616.min.js Show response
assets.adobedtm.com/0681c221600c/6fc9b54f3c25/
439 KB
130 KB
103ms
23ms
Script
application/x-javascript
2a02:26f0:2780:a9e::1e80
AKAMAI-ASN1 Akama...
General
Full URL
https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/launch-4756de8c2616.min.js
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/pf/resources/dist/js/main.js?d=1025&mxId=00000000
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:2780:a9e::1e80 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
AkamaiNetStorage /
Resource Hash
3dc9dbaedcce7656d7e5f2121902728ed4327d1f0f197a10d90e4f219ed6c738
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=3600
timing-allow-origin
*
content-encoding
gzip
etag
"7bba7d80b8254357829f412a1b5179be:1790086490.862792"
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 19:57:05 GMT
accept-ranges
bytes
access-control-allow-origin
https://los40.com.pa
content-length
132948
date
Thu, 01 Oct 2026 18:57:05 GMT
content-type
application/x-javascript
last-modified
Tue, 22 Sep 2026 14:14:50 GMT
server
AkamaiNetStorage
vary
Accept-Encoding
GET
H2
200
/ Show response
prra.spxl.socy.es/pixel/js/L40P3qKlFpP589/
23 KB
10 KB
147ms
40ms
Script
application/javascript
178.33.150.172
OVH OVH SAS
General
Full URL
https://prra.spxl.socy.es/pixel/js/L40P3qKlFpP589/
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/pf/resources/dist/js/main.js?d=1025&mxId=00000000
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
178.33.150.172 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
ip172.ip-178-33-150.eu
Software
Microsoft-IIS/7.5 / ASP.NET
Resource Hash
d9f120ed9ded67f4ac4db35c78e4683e05a7bea813e91edf6771f95e41f068e0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

access-control-expose-headers
Expires,Cache-Control,X-Accel-Expires,Content-Type,Access-Control-Allow-Origin
content-encoding
gzip
age
43
access-control-allow-methods
GET,POST,HEAD,OPTIONS
expires
Thu, 01 Oct 2026 19:06:22 GMT
x-do-cache
true
date
Thu, 01 Oct 2026 18:56:22 GMT
content-type
application/javascript; charset=utf-8
vary
Accept-Encoding
access-control-allow-headers
DNT,X-CustomHeader,Keep-Alive,User-Agent,X-Requested-With,If-Modified-Since,Cache-Control,Content-Type,Authorization,Referer,Accept
x-cache-status
HIT
x-aspnet-version
4.0.30319
x-backend-addr
10.244.3.155
accept-ranges
bytes
access-control-allow-origin
*
x-powered-by
ASP.NET
server
Microsoft-IIS/7.5
HEAD
H3
200
adsbygoogle.js
pagead2.googlesyndication.com/pagead/js/
0
0
86ms
46ms
Fetch
text/javascript
142.251.14.155
Google LLC
General
Full URL
https://pagead2.googlesyndication.com/pagead/js/adsbygoogle.js
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/pf/resources/js/libs/persistent-player.min.js?d=1025&mxId=00000000
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.14.155 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f155.1e100.net
Software
cafe /
Resource Hash
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
etag
9449787078224857831
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 18:57:05 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
date
Thu, 01 Oct 2026 18:57:05 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-disposition
attachment; filename="f.txt"
link
<https://googleads.g.doubleclick.net>; rel="preconnect"; crossorigin
cache-control
private, max-age=3600, stale-while-revalidate=3600
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
content-length
57076
x-xss-protection
0
server
cafe
GET
H2
200
map-co.svg
los40.com.pa/pf/resources/dist/img/
127 KB
27 KB
28ms
28ms
Image
image/svg+xml
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/resources/dist/img/map-co.svg?d=1025&mxId=00000000
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/pf/resources/dist/css/los40-pa/bundle_all.css?d=1025&mxId=00000000
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
fee20f0ab7f9cf7681ff58e4107507c475c9c9c2a8204de11eead6da23a3356c
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/pf/resources/dist/css/los40-pa/bundle_all.css?d=1025&mxId=00000000
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
content-security-policy
upgrade-insecure-requests
cache-control
public, max-age=31536000
content-encoding
gzip
x-arc-ttl
31536000
etag
W/"ee26a572a4dec96baae54254d8a1ec0d"
expires
Fri, 01 Oct 2027 18:57:05 GMT
access-control-allow-origin
*
content-length
27596
date
Thu, 01 Oct 2026 18:57:05 GMT
x-arc-request-id
0.b2163017.1790881025.6096
content-type
image/svg+xml
last-modified
Thu, 01 Oct 2026 11:12:02 GMT
server
openresty
x-amz-server-side-encryption
AES256
GET
H2
200
www-player.css
www.youtube.com/s/player/8ab5c328/ Frame 8D10
532 KB
57 KB
24ms
22ms
Stylesheet
text/css
2001:4860:4826:400::
Google LLC
General
Full URL
https://www.youtube.com/s/player/8ab5c328/www-player.css
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/fRIhCiUVaKs
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:4826:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
3c9902065d76c2e9cf04e2d7555f6a3e2ff55f17f2956e3389dbdc836ff15d31
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/fRIhCiUVaKs
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
34336
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 09:24:49 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 09:24:49 GMT
last-modified
Wed, 30 Sep 2026 04:27:49 GMT
content-type
text/css
vary
Accept-Encoding, Origin
cache-control
public, max-age=31536000
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
58415
x-xss-protection
0
server
sffe
GET
H2
200
m=root,base
www.youtube.com/s/_/ytembeds/_/ss/k=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQADG/d=1/br=1/rs=AGKMywERbMQCr1fMaIql1mnFkXIPQZxLow/ Frame 8D10
10 KB
3 KB
39ms
37ms
Stylesheet
text/css
2001:4860:4826:400::
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/ss/k=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQADG/d=1/br=1/rs=AGKMywERbMQCr1fMaIql1mnFkXIPQZxLow/m=root,base
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/fRIhCiUVaKs
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:4826:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
aaea1928868e3ef330ab5278134bac85bd1074b1bb9ac4fa40159fb906b25557
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/fRIhCiUVaKs
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
22057
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 12:49:28 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 12:49:28 GMT
last-modified
Wed, 30 Sep 2026 19:08:25 GMT
content-type
text/css; charset=UTF-8
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
2381
x-xss-protection
0
server
sffe
GET
H3
200
KFO7CnqEu92Fr1ME7kSn66aGLdTylUAMa3yUBA.woff2
fonts.gstatic.com/s/roboto/v48/ Frame 8D10
39 KB
39 KB
58ms
26ms
Font
font/woff2
142.251.110.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/roboto/v48/KFO7CnqEu92Fr1ME7kSn66aGLdTylUAMa3yUBA.woff2
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/fRIhCiUVaKs
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.110.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f94.1e100.net
Software
sffe /
Resource Hash
20b535fa80c8189e3b87d1803038389960203a886d502bc2ef1857affc2f38d2
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://www.youtube.com
sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

age
31185
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 10:17:20 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 10:17:20 GMT
last-modified
Thu, 29 May 2025 23:30:55 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
40128
x-xss-protection
0
server
sffe
GET
H2
200
m=root,base Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQADG/d=1/excm=base,root/br=1/rs=AGKMywHPwBmNjDXkqTzY4KDK4LnhoANgJg/ Frame 8D10
469 KB
158 KB
35ms
34ms
Script
text/javascript
2001:4860:4826:400::
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQADG/d=1/excm=base,root/br=1/rs=AGKMywHPwBmNjDXkqTzY4KDK4LnhoANgJg/m=root,base
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/fRIhCiUVaKs
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:4826:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
d5e6ce5d020856b27b56efd756d0e313a4f6177adec408e1cf7dbebe70cea90a
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/fRIhCiUVaKs
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
22119
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 12:48:26 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 12:48:26 GMT
last-modified
Thu, 01 Oct 2026 03:06:41 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
161960
x-xss-protection
0
server
sffe
GET
H2
200
base.js Show response
www.youtube.com/s/player/8ab5c328/player_embed_es6.vflset/de_DE/ Frame 8D10
2 MB
475 KB
46ms
46ms
Script
text/javascript
2001:4860:4826:400::
Google LLC
General
Full URL
https://www.youtube.com/s/player/8ab5c328/player_embed_es6.vflset/de_DE/base.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/fRIhCiUVaKs
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:4826:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
db6ad205995da14e082e8522a7a82ca52aa824efdb0cad8dadbabf5ffca2faf1
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/fRIhCiUVaKs
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
127639
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Thu, 30 Sep 2027 07:29:46 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 30 Sep 2026 07:29:46 GMT
last-modified
Wed, 30 Sep 2026 04:27:49 GMT
content-type
text/javascript
vary
Accept-Encoding, Origin
cache-control
public, max-age=31536000
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
486502
x-xss-protection
0
server
sffe
GET
H2
200
www-player.css
www.youtube.com/s/player/8ab5c328/ Frame B420
532 KB
0
1ms
1ms
Stylesheet
text/css
2001:4860:4826:400::
Google LLC
General
Full URL
https://www.youtube.com/s/player/8ab5c328/www-player.css
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/_1W51TfwOEA
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:4826:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
3c9902065d76c2e9cf04e2d7555f6a3e2ff55f17f2956e3389dbdc836ff15d31
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/_1W51TfwOEA
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
34336
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 09:24:49 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 09:24:49 GMT
last-modified
Wed, 30 Sep 2026 04:27:49 GMT
content-type
text/css
vary
Accept-Encoding, Origin
cache-control
public, max-age=31536000
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
58415
x-xss-protection
0
server
sffe
GET
H2
200
m=root,base
www.youtube.com/s/_/ytembeds/_/ss/k=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/br=1/rs=AGKMywG-lxu8F22vbSId3KyWJKWKvkEUvg/ Frame B420
0
53 B
53ms
52ms
Stylesheet
text/css
2001:4860:4826:400::
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/ss/k=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/br=1/rs=AGKMywG-lxu8F22vbSId3KyWJKWKvkEUvg/m=root,base
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/_1W51TfwOEA
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:4826:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/_1W51TfwOEA
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

age
22119
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 12:48:26 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 12:48:26 GMT
last-modified
Wed, 30 Sep 2026 19:08:25 GMT
content-type
text/css; charset=UTF-8
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
0
x-xss-protection
0
server
sffe
GET
H3
200
KFO7CnqEu92Fr1ME7kSn66aGLdTylUAMa3yUBA.woff2
fonts.gstatic.com/s/roboto/v48/ Frame B420
39 KB
0
50ms
50ms
Font
font/woff2
142.251.110.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/roboto/v48/KFO7CnqEu92Fr1ME7kSn66aGLdTylUAMa3yUBA.woff2
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/_1W51TfwOEA
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.110.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f94.1e100.net
Software
sffe /
Resource Hash
20b535fa80c8189e3b87d1803038389960203a886d502bc2ef1857affc2f38d2
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://www.youtube.com
sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

age
31185
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 10:17:20 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 10:17:20 GMT
last-modified
Thu, 29 May 2025 23:30:55 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
40128
x-xss-protection
0
server
sffe
GET
H3
200
m=root,base Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/ Frame B420
458 KB
156 KB
22ms
20ms
Script
text/javascript
142.251.154.4
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/_1W51TfwOEA
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.154.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
43f040f22fdc551d207513b8e2b7be100273ff01f221dbdbb95e0d3cee9ba2b8
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/_1W51TfwOEA
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
22072
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 12:49:13 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 12:49:13 GMT
last-modified
Thu, 01 Oct 2026 03:06:41 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
159418
x-xss-protection
0
server
sffe
GET
H2
200
base.js Show response
www.youtube.com/s/player/8ab5c328/player_embed_es6.vflset/de_DE/ Frame B420
2 MB
0
15ms
15ms
Script
text/javascript
2001:4860:4826:400::
Google LLC
General
Full URL
https://www.youtube.com/s/player/8ab5c328/player_embed_es6.vflset/de_DE/base.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/_1W51TfwOEA
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:4826:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
db6ad205995da14e082e8522a7a82ca52aa824efdb0cad8dadbabf5ffca2faf1
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/_1W51TfwOEA
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
127639
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Thu, 30 Sep 2027 07:29:46 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 30 Sep 2026 07:29:46 GMT
last-modified
Wed, 30 Sep 2026 04:27:49 GMT
content-type
text/javascript
vary
Accept-Encoding, Origin
cache-control
public, max-age=31536000
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
486502
x-xss-protection
0
server
sffe
GET
H2
200
core.css
player.prisamedia.com/core//style/
10 KB
2 KB
25ms
23ms
Stylesheet
text/css
199.232.198.133
Fastly
General
Full URL
https://player.prisamedia.com/core//style/core.css
Requested by
Host: player.prisamedia.com
URL: https://player.prisamedia.com/core//js/coreplayer.min.js
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
199.232.198.133 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
/
Resource Hash
ba0973764311004cc5ff9f86b80bd10881e90057c7c0f2716bbbfb08cd35a373

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
"11ab1fa1ff29a9afb62d5be52131e804"
age
22826
x-timer
S1790881025.287319,VS0,VE0
via
1.1 varnish
accept-ranges
bytes
access-control-allow-origin
*
x-cache
HIT
content-length
2403
date
Thu, 01 Oct 2026 18:57:05 GMT
last-modified
Thu, 01 Oct 2026 12:36:34 GMT
content-type
text/css; charset=utf-8
x-served-by
cache-lin1730051-LIN
x-cache-hits
3
vary
Accept-Encoding
GET
H2
200
561 Show response
fapi-top.prisasd.com/api/null/player/
714 B
700 B
84ms
22ms
Fetch
application/json
199.232.198.133
Fastly
General
Full URL
https://fapi-top.prisasd.com/api/null/player/561?ignoreAccount
Requested by
Host: player.prisamedia.com
URL: https://player.prisamedia.com/core//js/coreplayer.min.js
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
199.232.198.133 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
Apache/2.2.15 (CentOS) / PHP/7.1.9
Resource Hash
7c63466de3d85a30131cfc8ca195ae5b839883c2f4dcf5bad4ca3265fa4ae076

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
age
869
x-cache
MISS, HIT, HIT
date
Thu, 01 Oct 2026 18:57:05 GMT
content-type
application/json
vary
Accept-Encoding
x-cache-hits
2, 0
x-served-by
cache-mad22023-MAD, cache-lin1730044-LIN
cache-control
max-age=60, public
x-timer
S1790881025.352364,VS0,VE1
via
1.1 varnish, 1.1 google, 1.1 varnish, 1.1 varnish
accept-ranges
bytes
access-control-allow-origin
*
content-length
409
x-powered-by
PHP/7.1.9
server
Apache/2.2.15 (CentOS)
GET
H2
200
www-player.css
www.youtube.com/s/player/8ab5c328/ Frame CCE2
532 KB
0
1ms
1ms
Stylesheet
text/css
2001:4860:4826:400::
Google LLC
General
Full URL
https://www.youtube.com/s/player/8ab5c328/www-player.css
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/s3a4OQR-10M
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:4826:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
3c9902065d76c2e9cf04e2d7555f6a3e2ff55f17f2956e3389dbdc836ff15d31
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://www.youtube.com/embed/s3a4OQR-10M

Response headers

content-encoding
br
age
34336
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 09:24:49 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 09:24:49 GMT
last-modified
Wed, 30 Sep 2026 04:27:49 GMT
content-type
text/css
vary
Accept-Encoding, Origin
cache-control
public, max-age=31536000
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
58415
x-xss-protection
0
server
sffe
GET
H2
200
m=root,base
www.youtube.com/s/_/ytembeds/_/ss/k=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/br=1/rs=AGKMywG-lxu8F22vbSId3KyWJKWKvkEUvg/ Frame CCE2
0
0
53ms
52ms
Stylesheet
text/css
2001:4860:4826:400::
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/ss/k=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/br=1/rs=AGKMywG-lxu8F22vbSId3KyWJKWKvkEUvg/m=root,base
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/s3a4OQR-10M
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:4826:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://www.youtube.com/embed/s3a4OQR-10M

Response headers

age
22119
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 12:48:26 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 12:48:26 GMT
last-modified
Wed, 30 Sep 2026 19:08:25 GMT
content-type
text/css; charset=UTF-8
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
0
x-xss-protection
0
server
sffe
GET
H3
200
KFO7CnqEu92Fr1ME7kSn66aGLdTylUAMa3yUBA.woff2
fonts.gstatic.com/s/roboto/v48/ Frame CCE2
39 KB
0
50ms
50ms
Font
font/woff2
142.251.110.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/roboto/v48/KFO7CnqEu92Fr1ME7kSn66aGLdTylUAMa3yUBA.woff2
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/s3a4OQR-10M
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.110.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f94.1e100.net
Software
sffe /
Resource Hash
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://www.youtube.com
Referer
https://www.youtube.com/

Response headers

age
31185
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 10:17:20 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 10:17:20 GMT
last-modified
Thu, 29 May 2025 23:30:55 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
40128
x-xss-protection
0
server
sffe
GET
H3
200
m=root,base Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/ Frame CCE2
458 KB
0
0ms
0ms
Script
text/javascript
142.251.154.4
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/s3a4OQR-10M
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.154.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
43f040f22fdc551d207513b8e2b7be100273ff01f221dbdbb95e0d3cee9ba2b8
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/s3a4OQR-10M
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
22072
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 12:49:13 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 12:49:13 GMT
last-modified
Thu, 01 Oct 2026 03:06:41 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
159418
x-xss-protection
0
server
sffe
GET
H2
200
base.js Show response
www.youtube.com/s/player/8ab5c328/player_embed_es6.vflset/de_DE/ Frame CCE2
2 MB
0
1ms
1ms
Script
text/javascript
2001:4860:4826:400::
Google LLC
General
Full URL
https://www.youtube.com/s/player/8ab5c328/player_embed_es6.vflset/de_DE/base.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/s3a4OQR-10M
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:4826:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
db6ad205995da14e082e8522a7a82ca52aa824efdb0cad8dadbabf5ffca2faf1
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/s3a4OQR-10M
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
127639
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Thu, 30 Sep 2027 07:29:46 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 30 Sep 2026 07:29:46 GMT
last-modified
Wed, 30 Sep 2026 04:27:49 GMT
content-type
text/javascript
vary
Accept-Encoding, Origin
cache-control
public, max-age=31536000
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
486502
x-xss-protection
0
server
sffe
GET
H2
200
40_principales Show response
fapi-top.prisasd.com/api/v2/search/los40panama/audio/idref/
2 KB
990 B
23ms
21ms
Fetch
application/json
199.232.198.133
Fastly
General
Full URL
https://fapi-top.prisasd.com/api/v2/search/los40panama/audio/idref/40_principales?player_info=true
Requested by
Host: player.prisamedia.com
URL: https://player.prisamedia.com/core//js/coreplayer.min.js
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
199.232.198.133 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
Apache/2.2.15 (CentOS) / PHP/7.1.9
Resource Hash
39da84904cb9b1c7179ab587e50a28037066fc25f4c494b9f10c6c8710c7ee4c

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
age
867
x-cache
MISS, HIT, HIT
date
Thu, 01 Oct 2026 18:57:05 GMT
content-type
application/json
vary
Accept-Encoding
x-cache-hits
1, 0
x-served-by
cache-mad2200127-MAD, cache-lin1730044-LIN
cache-control
max-age=100, public
x-timer
S1790881025.381702,VS0,VE1
via
1.1 varnish, 1.1 google, 1.1 varnish, 1.1 varnish
accept-ranges
bytes
access-control-allow-origin
*
content-length
872
x-powered-by
PHP/7.1.9
server
Apache/2.2.15 (CentOS)
GET
H2
200
rd Show response
dpm.demdex.net/id/
Redirect Chain
  • https://dpm.demdex.net/id?d_visid_ver=5.4.0&d_fieldgroup=MC&d_rtbd=json&d_ver=2&d_verify=1&d_orgid=2387401053DB208C0A490D4C%40AdobeOrg&d_nsid=0&ts=1790881025393
  • https://dpm.demdex.net/id/rd?d_visid_ver=5.4.0&d_fieldgroup=MC&d_rtbd=json&d_ver=2&d_verify=1&d_orgid=2387401053DB208C0A490D4C%40AdobeOrg&d_nsid=0&ts=1790881025393
1 KB
1 KB
50ms
50ms
XHR
application/json
52.30.159.196
Amazon.com
General
Full URL
https://dpm.demdex.net/id/rd?d_visid_ver=5.4.0&d_fieldgroup=MC&d_rtbd=json&d_ver=2&d_verify=1&d_orgid=2387401053DB208C0A490D4C%40AdobeOrg&d_nsid=0&ts=1790881025393
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Server
52.30.159.196 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-52-30-159-196.eu-west-1.compute.amazonaws.com
Software
/
Resource Hash
2405c568804ff70ec4366ff13f20dc1adbd8acdce151e8a57784765656095ce9
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
Referer
https://los40.com.pa/

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
no-cache,no-store,must-revalidate,max-age=0,proxy-revalidate,no-transform,private
dcs
dcs-prod-irl1-2-v097-02f3e6dfa.edge-irl1.demdex.com 4 ms
content-encoding
zstd
pragma
no-cache
access-control-allow-credentials
true
x-tid
xupVoQUS7CE=
expires
Thu, 01 Jan 1970 00:00:00 UTC
access-control-allow-origin
https://los40.com.pa
content-length
702
p3p
policyref="/w3c/p3p.xml", CP="NOI NID CURa ADMa DEVa PSAa PSDa OUR SAMa BUS PUR COM NAV INT"
date
Thu, 01 Oct 2026 18:57:05 GMT
content-type
application/json;charset=utf-8
vary
Origin

Redirect headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
no-cache,no-store,must-revalidate,max-age=0,proxy-revalidate,no-transform,private
location
https://dpm.demdex.net/id/rd?d_visid_ver=5.4.0&d_fieldgroup=MC&d_rtbd=json&d_ver=2&d_verify=1&d_orgid=2387401053DB208C0A490D4C%40AdobeOrg&d_nsid=0&ts=1790881025393
dcs
dcs-prod-irl1-2-v097-09c1d7e2e.edge-irl1.demdex.com 0 ms
pragma
no-cache
access-control-allow-credentials
true
x-tid
dXxzcEoxL1I=
expires
Thu, 01 Jan 1970 00:00:00 UTC
access-control-allow-origin
https://los40.com.pa
content-length
0
p3p
policyref="/w3c/p3p.xml", CP="NOI NID CURa ADMa DEVa PSAa PSDa OUR SAMa BUS PUR COM NAV INT"
date
Thu, 01 Oct 2026 18:57:05 GMT
vary
Origin
GET
H2
200
AppMeasurement.min.js Show response
assets.adobedtm.com/extensions/EP171e731c9ba34f1c950c36d26e3efd61/
33 KB
12 KB
24ms
22ms
Script
application/x-javascript
2a02:26f0:2780:a9e::1e80
AKAMAI-ASN1 Akama...
General
Full URL
https://assets.adobedtm.com/extensions/EP171e731c9ba34f1c950c36d26e3efd61/AppMeasurement.min.js
Requested by
Host: assets.adobedtm.com
URL: https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/launch-4756de8c2616.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:2780:a9e::1e80 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
AkamaiNetStorage /
Resource Hash
9219086b4f2c3bf77854b2e06ccd97ad32b9b7a140e65ff8b974a3bae6c7854c
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache
timing-allow-origin
*
content-encoding
gzip
etag
"d860c16ac938f7d839f0ec158d02d0f0:1644856531.418573"
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 19:57:05 GMT
accept-ranges
bytes
access-control-allow-origin
https://los40.com.pa
content-length
12163
date
Thu, 01 Oct 2026 18:57:05 GMT
content-type
application/x-javascript
last-modified
Mon, 14 Feb 2022 16:35:31 GMT
server
AkamaiNetStorage
vary
Accept-Encoding
GET
H2
200
AppMeasurement_Module_ActivityMap.min.js Show response
assets.adobedtm.com/extensions/EP171e731c9ba34f1c950c36d26e3efd61/
3 KB
2 KB
23ms
22ms
Script
application/x-javascript
2a02:26f0:2780:a9e::1e80
AKAMAI-ASN1 Akama...
General
Full URL
https://assets.adobedtm.com/extensions/EP171e731c9ba34f1c950c36d26e3efd61/AppMeasurement_Module_ActivityMap.min.js
Requested by
Host: assets.adobedtm.com
URL: https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/launch-4756de8c2616.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:2780:a9e::1e80 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
AkamaiNetStorage /
Resource Hash
462a66acbf50e933685e7587e9f1441df8225b2bb4d6b7bc5e757eccf4ff6575
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache
timing-allow-origin
*
content-encoding
gzip
etag
"2d1382c349d480b6b41574ac0c1af066:1644856531.739514"
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 19:57:05 GMT
accept-ranges
bytes
access-control-allow-origin
https://los40.com.pa
content-length
1597
date
Thu, 01 Oct 2026 18:57:05 GMT
content-type
application/x-javascript
last-modified
Mon, 14 Feb 2022 16:35:31 GMT
server
AkamaiNetStorage
vary
Accept-Encoding
GET
H3
200
id Show response
googleads.g.doubleclick.net/pagead/ Frame 8D10
Redirect Chain
  • https://googleads.g.doubleclick.net/pagead/id
  • https://googleads.g.doubleclick.net/pagead/id?slf_rd=1
100 B
146 B
61ms
61ms
XHR
application/json
142.251.110.154
Google LLC
General
Full URL
https://googleads.g.doubleclick.net/pagead/id?slf_rd=1
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/fRIhCiUVaKs
Protocol
H3
Server
142.251.110.154 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f154.1e100.net
Software
cafe /
Resource Hash
33980143bfbab156ea95543a0982dc303283902811f193dcb20a94ce55411021
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
Referer
https://www.youtube.com/

Response headers

content-encoding
gzip
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
date
Thu, 01 Oct 2026 18:57:05 GMT
content-type
application/json; charset=UTF-8
content-disposition
attachment; filename="f.txt"
cache-control
no-cache, no-store, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
access-control-allow-origin
https://www.youtube.com
content-length
120
x-xss-protection
0
server
cafe

Redirect headers

x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
date
Thu, 01 Oct 2026 18:57:05 GMT
content-type
text/html; charset=UTF-8
cache-control
no-cache, no-store, must-revalidate
location
https://googleads.g.doubleclick.net/pagead/id?slf_rd=1
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
access-control-allow-origin
https://www.youtube.com
content-length
0
x-xss-protection
0
server
cafe
GET
H2
200
ad_status.js Show response
static.doubleclick.net/instream/ Frame 8D10
29 B
495 B
83ms
23ms
Script
text/javascript
2a00:1450:4001:c15::95
Google LLC
General
Full URL
https://static.doubleclick.net/instream/ad_status.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQADG/d=1/excm=base,root/br=1/rs=AGKMywHPwBmNjDXkqTzY4KDK4LnhoANgJg/m=root,base
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a00:1450:4001:c15::95 Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
eed0dc1fdb5d97ed188ae16fd5e1024a5bb744af47340346be2146300a6c54b9
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

age
782
report-to
{"group":"ads-doubleclick-media","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/ads-doubleclick-media"}]}
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 18:59:03 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 18:44:03 GMT
last-modified
Thu, 12 Dec 2013 23:40:16 GMT
content-type
text/javascript
cache-control
public, max-age=900
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to="ads-doubleclick-media"
content-length
29
x-xss-protection
0
server
sffe
GET
H3
200
m=r78Drb Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/ck=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQADG/d=1/exm=base,root/excm=base,root/ed=1/br=1/rs=AGKMywE-IAOb1-WuZ5ii0tpi9f-56... Frame 8D10
917 KB
220 KB
18ms
17ms
Script
text/javascript
142.251.154.4
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/ck=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQADG/d=1/exm=base,root/excm=base,root/ed=1/br=1/rs=AGKMywE-IAOb1-WuZ5ii0tpi9f-56d9aig/m=r78Drb
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQADG/d=1/excm=base,root/br=1/rs=AGKMywHPwBmNjDXkqTzY4KDK4LnhoANgJg/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.154.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
5b275c116242b1da62a2f7e05ee653d88a6d94e3ba3e65a34d6368274e9f20c9
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/fRIhCiUVaKs
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
22057
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 12:49:28 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 12:49:28 GMT
last-modified
Wed, 30 Sep 2026 19:08:25 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
225076
x-xss-protection
0
server
sffe
GET
H2
200
radio-api-program-schedules Show response
los40.com.pa/pf/api/v3/content/fetch/
6 KB
2 KB
664ms
664ms
Fetch
application/json
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/api/v3/content/fetch/radio-api-program-schedules?query=%7B%22radioStationId%22%3A%22025000%22%2C%22date%22%3A%222026-10-01T20%3A57%3A00%2B02%3A00%22%2C%22cutTypeCode%22%3A%22Rec_720x720%22%2C%22withAudios%22%3Afalse%7D&d=1025
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/pf/resources/js/libs/persistent-player.min.js?d=1025&mxId=00000000
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
bda621fbe7c839069883292a99bbd863f226600faf1a62b971e045c629141b5a
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
Accept
application/json
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-security-policy
upgrade-insecure-requests
cache-control
max-age=120
content-encoding
gzip
x-arc-ttl
120
etag
W/"1963-2dgNFevm8RHF4sT8Oxf0b9FTp08"
x-arc-pb-request-id
3d5db84f-08ee-44a3-b6ba-8f1a20c9453d
expires
Thu, 01 Oct 2026 18:59:06 GMT
content-length
1264
date
Thu, 01 Oct 2026 18:57:06 GMT
x-arc-request-id
0.b2163017.1790881025.61bd
content-type
application/json; charset=utf-8
vary
Accept-Encoding
server
openresty
last-modified
Thu, 01 Oct 2026 18:57:05 GMT
GET
H3
200
id Show response
googleads.g.doubleclick.net/pagead/ Frame CCE2
Redirect Chain
  • https://googleads.g.doubleclick.net/pagead/id
  • https://googleads.g.doubleclick.net/pagead/id?slf_rd=1
100 B
146 B
64ms
63ms
XHR
application/json
142.251.110.154
Google LLC
General
Full URL
https://googleads.g.doubleclick.net/pagead/id?slf_rd=1
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/s3a4OQR-10M
Protocol
H3
Server
142.251.110.154 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f154.1e100.net
Software
cafe /
Resource Hash
62ffc2a6642875e95ce9c8e75eac2c4320d32be120823e5d807b757e4d72e73d
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
Referer
https://www.youtube.com/

Response headers

content-encoding
gzip
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
date
Thu, 01 Oct 2026 18:57:05 GMT
content-type
application/json; charset=UTF-8
content-disposition
attachment; filename="f.txt"
cache-control
no-cache, no-store, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
access-control-allow-origin
https://www.youtube.com
content-length
120
x-xss-protection
0
server
cafe

Redirect headers

x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
date
Thu, 01 Oct 2026 18:57:05 GMT
content-type
text/html; charset=UTF-8
cache-control
no-cache, no-store, must-revalidate
location
https://googleads.g.doubleclick.net/pagead/id?slf_rd=1
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
access-control-allow-origin
https://www.youtube.com
content-length
0
x-xss-protection
0
server
cafe
GET
H2
200
ad_status.js Show response
static.doubleclick.net/instream/ Frame CCE2
29 B
0
72ms
72ms
Script
text/javascript
2a00:1450:4001:c15::95
Google LLC
General
Full URL
https://static.doubleclick.net/instream/ad_status.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a00:1450:4001:c15::95 Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
eed0dc1fdb5d97ed188ae16fd5e1024a5bb744af47340346be2146300a6c54b9
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

age
782
report-to
{"group":"ads-doubleclick-media","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/ads-doubleclick-media"}]}
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 18:59:03 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 18:44:03 GMT
last-modified
Thu, 12 Dec 2013 23:40:16 GMT
content-type
text/javascript
cache-control
public, max-age=900
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to="ads-doubleclick-media"
content-length
29
x-xss-protection
0
server
sffe
GET
H3
200
m=r78Drb Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/ck=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/exm=base,root/excm=base,root/ed=1/br=1/rs=AGKMywESyf9Y9X87KVWSKj1IXnBDyFL... Frame CCE2
914 KB
221 KB
24ms
24ms
Script
text/javascript
142.251.154.4
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/ck=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/exm=base,root/excm=base,root/ed=1/br=1/rs=AGKMywESyf9Y9X87KVWSKj1IXnBDyFLpDQ/m=r78Drb
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.154.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
ca01e9635150b32eea34bab004744a814e45a564585eeb9a572af2120e9091c4
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/s3a4OQR-10M
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
22072
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 12:49:13 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 12:49:13 GMT
last-modified
Wed, 30 Sep 2026 19:08:25 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
226102
x-xss-protection
0
server
sffe
GET
H3
200
id Show response
googleads.g.doubleclick.net/pagead/ Frame B420
Redirect Chain
  • https://googleads.g.doubleclick.net/pagead/id
  • https://googleads.g.doubleclick.net/pagead/id?slf_rd=1
100 B
146 B
102ms
61ms
XHR
application/json
142.251.110.154
Google LLC
General
Full URL
https://googleads.g.doubleclick.net/pagead/id?slf_rd=1
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/_1W51TfwOEA
Protocol
H3
Server
142.251.110.154 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f154.1e100.net
Software
cafe /
Resource Hash
b7aa1d267416afc8f3a744dd935be2fbf102e0dedc767582bfb404cfdd9017f5
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
Referer
https://www.youtube.com/

Response headers

content-encoding
gzip
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
date
Thu, 01 Oct 2026 18:57:05 GMT
content-type
application/json; charset=UTF-8
content-disposition
attachment; filename="f.txt"
cache-control
no-cache, no-store, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
access-control-allow-origin
https://www.youtube.com
content-length
120
x-xss-protection
0
server
cafe

Redirect headers

x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
date
Thu, 01 Oct 2026 18:57:05 GMT
content-type
text/html; charset=UTF-8
cache-control
no-cache, no-store, must-revalidate
location
https://googleads.g.doubleclick.net/pagead/id?slf_rd=1
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
access-control-allow-origin
https://www.youtube.com
content-length
0
x-xss-protection
0
server
cafe
GET
H2
200
ad_status.js Show response
static.doubleclick.net/instream/ Frame B420
29 B
0
64ms
64ms
Script
text/javascript
2a00:1450:4001:c15::95
Google LLC
General
Full URL
https://static.doubleclick.net/instream/ad_status.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a00:1450:4001:c15::95 Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
eed0dc1fdb5d97ed188ae16fd5e1024a5bb744af47340346be2146300a6c54b9
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

age
782
report-to
{"group":"ads-doubleclick-media","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/ads-doubleclick-media"}]}
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 18:59:03 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 18:44:03 GMT
last-modified
Thu, 12 Dec 2013 23:40:16 GMT
content-type
text/javascript
cache-control
public, max-age=900
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to="ads-doubleclick-media"
content-length
29
x-xss-protection
0
server
sffe
GET
H3
200
m=r78Drb Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/ck=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/exm=base,root/excm=base,root/ed=1/br=1/rs=AGKMywESyf9Y9X87KVWSKj1IXnBDyFL... Frame B420
914 KB
0
17ms
17ms
Script
text/javascript
142.251.154.4
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/ck=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/exm=base,root/excm=base,root/ed=1/br=1/rs=AGKMywESyf9Y9X87KVWSKj1IXnBDyFLpDQ/m=r78Drb
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.154.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
ca01e9635150b32eea34bab004744a814e45a564585eeb9a572af2120e9091c4
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/_1W51TfwOEA
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
22072
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 12:49:13 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 12:49:13 GMT
last-modified
Wed, 30 Sep 2026 19:08:25 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
226102
x-xss-protection
0
server
sffe
GET
H3
200
IOrCYK67i4VYhCfTkVQuJXe8pgp3Pb6j3OzRFUdhqF4.js Show response
www.google.com/js/th/ Frame 8D10
63 KB
24 KB
49ms
17ms
Script
text/javascript
142.251.155.119
Google LLC
General
Full URL
https://www.google.com/js/th/IOrCYK67i4VYhCfTkVQuJXe8pgp3Pb6j3OzRFUdhqF4.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQADG/d=1/excm=base,root/br=1/rs=AGKMywHPwBmNjDXkqTzY4KDK4LnhoANgJg/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.155.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
20eac260aebb8b85588427d391542e2577bca60a773dbea3dcecd1154761a85e
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
116226
report-to
{"group":"botguard-scs","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/botguard-scs"}]}
x-content-type-options
nosniff
expires
Thu, 30 Sep 2027 10:39:59 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 30 Sep 2026 10:39:59 GMT
last-modified
Mon, 28 Sep 2026 10:30:00 GMT
content-type
text/javascript
vary
Accept-Encoding
cache-control
public, max-age=31536000
cross-origin-opener-policy
same-origin; report-to="botguard-scs"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/botguard-scs
accept-ranges
bytes
content-length
24763
x-xss-protection
0
server
sffe
GET
H3
200
kmerDVxozI-rEkQjj3OA3wf3AFJmDzlT6Ha7IOTh4_A.js Show response
www.google.com/js/th/ Frame CCE2
61 KB
24 KB
22ms
18ms
Script
text/javascript
142.251.155.119
Google LLC
General
Full URL
https://www.google.com/js/th/kmerDVxozI-rEkQjj3OA3wf3AFJmDzlT6Ha7IOTh4_A.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.155.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
9267ab0d5c68cc8fab1244238f7380df07f70052660f3953e876bb20e4e1e3f0
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
112705
report-to
{"group":"botguard-scs","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/botguard-scs"}]}
x-content-type-options
nosniff
expires
Thu, 30 Sep 2027 11:38:40 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 30 Sep 2026 11:38:40 GMT
last-modified
Mon, 21 Sep 2026 12:30:00 GMT
content-type
text/javascript
vary
Accept-Encoding
cache-control
public, max-age=31536000
cross-origin-opener-policy
same-origin; report-to="botguard-scs"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/botguard-scs
accept-ranges
bytes
content-length
24255
x-xss-protection
0
server
sffe
GET
H3
200
IOrCYK67i4VYhCfTkVQuJXe8pgp3Pb6j3OzRFUdhqF4.js Show response
www.google.com/js/th/ Frame B420
63 KB
0
0ms
0ms
Script
text/javascript
142.251.155.119
Google LLC
General
Full URL
https://www.google.com/js/th/IOrCYK67i4VYhCfTkVQuJXe8pgp3Pb6j3OzRFUdhqF4.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.155.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
20eac260aebb8b85588427d391542e2577bca60a773dbea3dcecd1154761a85e
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
116226
report-to
{"group":"botguard-scs","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/botguard-scs"}]}
x-content-type-options
nosniff
expires
Thu, 30 Sep 2027 10:39:59 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 30 Sep 2026 10:39:59 GMT
last-modified
Mon, 28 Sep 2026 10:30:00 GMT
content-type
text/javascript
vary
Accept-Encoding
cache-control
public, max-age=31536000
cross-origin-opener-policy
same-origin; report-to="botguard-scs"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/botguard-scs
accept-ranges
bytes
content-length
24763
x-xss-protection
0
server
sffe
GET
H3
200
m=cwx9N Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/ck=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQADG/d=1/exm=base,r78Drb,root/excm=base,root/ed=1/br=1/rs=AGKMywE-IAOb1-WuZ5ii0t... Frame 8D10
60 KB
16 KB
17ms
17ms
Script
text/javascript
142.251.155.119
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/ck=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQADG/d=1/exm=base,r78Drb,root/excm=base,root/ed=1/br=1/rs=AGKMywE-IAOb1-WuZ5ii0tpi9f-56d9aig/m=cwx9N
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQADG/d=1/excm=base,root/br=1/rs=AGKMywHPwBmNjDXkqTzY4KDK4LnhoANgJg/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.155.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
08eaed4a37f8ae323b8a0faf40ade34714604fd86825ecc0453fb0c71efc6fd3
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/fRIhCiUVaKs
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
21222
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 13:03:23 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 13:03:23 GMT
last-modified
Wed, 30 Sep 2026 19:08:25 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
16052
x-xss-protection
0
server
sffe
GET
H3
200
m=cwx9N Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/ck=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/exm=base,r78Drb,root/excm=base,root/ed=1/br=1/rs=AGKMywESyf9Y9X87KVWSKj1I... Frame B420
60 KB
16 KB
18ms
18ms
Script
text/javascript
142.251.155.119
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/ck=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/exm=base,r78Drb,root/excm=base,root/ed=1/br=1/rs=AGKMywESyf9Y9X87KVWSKj1IXnBDyFLpDQ/m=cwx9N
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.155.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
a4a51f4bfe4bd295d2a57cb9a791fa3a5749f45b3d3ae05b518dfc410883650e
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/_1W51TfwOEA
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
21600
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 12:57:05 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 12:57:05 GMT
last-modified
Wed, 30 Sep 2026 19:08:25 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
15913
x-xss-protection
0
server
sffe
GET
H3
200
m=cwx9N Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/ck=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/exm=base,r78Drb,root/excm=base,root/ed=1/br=1/rs=AGKMywESyf9Y9X87KVWSKj1I... Frame CCE2
60 KB
0
0ms
0ms
Script
text/javascript
142.251.155.119
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/ck=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/exm=base,r78Drb,root/excm=base,root/ed=1/br=1/rs=AGKMywESyf9Y9X87KVWSKj1IXnBDyFLpDQ/m=cwx9N
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.155.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
a4a51f4bfe4bd295d2a57cb9a791fa3a5749f45b3d3ae05b518dfc410883650e
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/s3a4OQR-10M
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
21600
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 12:57:05 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 12:57:05 GMT
last-modified
Wed, 30 Sep 2026 19:08:25 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
15913
x-xss-protection
0
server
sffe
GET
H2
200
sddefault.jpg
i.ytimg.com/vi/fRIhCiUVaKs/ Frame 8D10
29 KB
30 KB
83ms
25ms
Image
image/jpeg
2a00:1450:4001:c25::77
Google LLC
General
Full URL
https://i.ytimg.com/vi/fRIhCiUVaKs/sddefault.jpg
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/fRIhCiUVaKs
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a00:1450:4001:c25::77 Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
01fa6f87fff322f56611bd5393de9caa4c7d7b6a92a040d2f2cee6249147af5f
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

etag
"1786055734"
age
66
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 20:55:59 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 18:55:59 GMT
content-type
image/jpeg
cache-control
public, max-age=7200
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
30037
x-xss-protection
0
server
sffe
GET
H2
200
dest5.html Show response
prisacom.demdex.net/ Frame 0222
7 KB
3 KB
157ms
46ms
Document
text/html
52.17.233.147
Amazon.com
General
Full URL
https://prisacom.demdex.net/dest5.html?d_nsid=0
Requested by
Host: assets.adobedtm.com
URL: https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/launch-4756de8c2616.min.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
52.17.233.147 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-52-17-233-147.eu-west-1.compute.amazonaws.com
Software
/
Resource Hash
7bea17a80a61ed0f54248b4ffc4c718f7c8ff2619742577a73591d62ce074da8
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

Referer
https://los40.com.pa/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

accept-ranges
bytes
cache-control
no-cache,no-store,must-revalidate,max-age=0,proxy-revalidate,no-transform,private
content-encoding
zstd
content-type
text/html;charset=UTF-8
date
Thu, 01 Oct 2026 18:57:05 GMT
dcs
dcs-prod-irl1-1-v097-0467c301a.edge-irl1.demdex.com 0 ms
expires
Thu, 01 Jan 1970 00:00:00 UTC
last-modified
Wed, 30 Sep 2026 09:35:14 GMT
p3p
policyref="/w3c/p3p.xml", CP="NOI NID CURa ADMa DEVa PSAa PSDa OUR SAMa BUS PUR COM NAV INT"
pragma
no-cache
strict-transport-security
max-age=31536000; includeSubDomains
vary
accept-encoding
x-tid
B2NaNj3CbTo=
GET
H2
200
id Show response
smetrics.los40.com.pa/
48 B
456 B
211ms
32ms
XHR
application/x-javascript
63.140.62.120
Amazon.com
General
Full URL
https://smetrics.los40.com.pa/id?d_visid_ver=5.4.0&d_fieldgroup=A&mcorgid=2387401053DB208C0A490D4C%40AdobeOrg&mid=70586572863888596102702472168040448371&ts=1790881025753
Requested by
Host: assets.adobedtm.com
URL: https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/launch-4756de8c2616.min.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
63.140.62.120 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ip-63-140-62-120.data.adobedc.net
Software
jag /
Resource Hash
1c548847d5707fe6e7c95c678c0ad5a72b53e4e4000fdb1a49eae49dbe64528c
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
Content-Type
application/x-www-form-urlencoded
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
no-cache, no-store, max-age=0, no-transform, private
access-control-allow-credentials
true
x-content-type-options
nosniff
access-control-allow-origin
https://los40.com.pa
p3p
CP="This is not a P3P policy"
content-length
48
date
Thu, 01 Oct 2026 18:57:05 GMT
x-xss-protection
1; mode=block
content-type
application/x-javascript;charset=utf-8
vary
Origin
server
jag
POST
H2
200
delivery Show response
prisacom.tt.omtrdc.net/rest/v1/
351 B
830 B
147ms
59ms
XHR
application/json
63.140.62.200
Amazon.com
General
Full URL
https://prisacom.tt.omtrdc.net/rest/v1/delivery?client=prisacom&sessionId=8cf22a303489402fa3d06cfa2438692f&version=2.11.4
Requested by
Host: assets.adobedtm.com
URL: https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/launch-4756de8c2616.min.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
63.140.62.200 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ip-63-140-62-200.data.adobedc.net
Software
jag /
Resource Hash
516fce352bd44ae4987e9ee4cb538fced0ccad0ea7d26743320a3875337190e2
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
Content-Type
text/plain
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
x-request-id
091bb706-95a1-418b-867f-0aa01289ebfe
cache-control
no-cache, no-store, max-age=0, no-transform, private
timing-allow-origin
*
content-encoding
gzip
accept-ch
Sec-CH-UA, Sec-CH-UA-Arch, Sec-CH-UA-Model, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version, Sec-CH-UA-Mobile, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version-List
access-control-allow-credentials
true
referrer-policy
strict-origin-when-cross-origin
x-content-type-options
nosniff
access-control-allow-origin
https://los40.com.pa
date
Thu, 01 Oct 2026 18:57:05 GMT
x-xss-protection
1; mode=block
content-type
application/json;charset=UTF-8
vary
origin,access-control-request-method,access-control-request-headers,accept-encoding
server
jag
GET
H2
200
default.webp
i.ytimg.com/vi_webp/_1W51TfwOEA/ Frame B420
1 KB
1 KB
80ms
49ms
Image
image/webp
2a00:1450:4001:c25::77
Google LLC
General
Full URL
https://i.ytimg.com/vi_webp/_1W51TfwOEA/default.webp
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/_1W51TfwOEA
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a00:1450:4001:c25::77 Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
90e4b6619a37d75bbc2ee6a09bc664d93d559a6ada4c43591d940e47c03ebf6a
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
public, max-age=7200
etag
"1780345100"
cross-origin-resource-policy
cross-origin
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 20:57:05 GMT
accept-ranges
bytes
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
1220
date
Thu, 01 Oct 2026 18:57:05 GMT
x-xss-protection
0
content-type
image/webp
vary
Origin
server
sffe
GET
H2
200
default.jpg
i.ytimg.com/vi/s3a4OQR-10M/ Frame CCE2
3 KB
3 KB
58ms
49ms
Image
image/jpeg
2a00:1450:4001:c25::77
Google LLC
General
Full URL
https://i.ytimg.com/vi/s3a4OQR-10M/default.jpg
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/s3a4OQR-10M
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a00:1450:4001:c25::77 Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
4e450e74a3d680d3ff2de1ebd994eee8d653c336c8260b50059d5c1e0123d522
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

etag
"1756912348"
age
2453
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 20:16:12 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 18:16:12 GMT
content-type
image/jpeg
cache-control
public, max-age=7200
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
2707
x-xss-protection
0
server
sffe
GET
H2
200
sdk.2af281429ae434027f53ac77f93097d5b4488b76.js Show response
sdk.privacy-center.org/sdk/2af281429ae434027f53ac77f93097d5b4488b76/modern/
453 KB
116 KB
29ms
28ms
Script
application/javascript
2600:9000:28eb:1000:5:b7cc:d3c0:93a1
Amazon.com
General
Full URL
https://sdk.privacy-center.org/sdk/2af281429ae434027f53ac77f93097d5b4488b76/modern/sdk.2af281429ae434027f53ac77f93097d5b4488b76.js
Requested by
Host: sdk.privacy-center.org
URL: https://sdk.privacy-center.org/8ba38674-edba-484d-8053-435051d79f72/loader.js?target=los40.com.pa
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2600:9000:28eb:1000:5:b7cc:d3c0:93a1 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
Software
AmazonS3 /
Resource Hash
6b8708480876814fcce40a6aad216e047a2f780a3a958bd8d9261c68b131f5e7

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
cache-control
public, max-age=31536000
content-encoding
br
etag
W/"ce3a3de5ea4713f6544c9732e8c95b78-1"
age
104516
via
1.1 90a1c9bfae56eb9062f3a496d1877f0c.cloudfront.net (CloudFront)
alt-svc
h3=":443"; ma=86400
x-cache
Hit from cloudfront
x-amz-cf-id
nmXKdhbHshoyYtiOT51slo8AvWW0nVsKKEr7MSjZP-2sCZ7uou8PiQ==
date
Wed, 30 Sep 2026 13:55:10 GMT
content-type
application/javascript; charset=utf-8
last-modified
Wed, 30 Sep 2026 13:55:01 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P12
x-amz-server-side-encryption
AES256
GET
H2
200
pixel.json Show response
prra.spxl.socy.es/
715 B
1 KB
116ms
40ms
XHR
application/json
178.33.150.172
OVH OVH SAS
General
Full URL
https://prra.spxl.socy.es/pixel.json?t=L40P3qKlFpP589&r=&h=https%3A%2F%2Flos40.com.pa%2Fhomepage&_ga=&_gid=&_uid=bs.1.0.BGdiUJ4WGmij&_tcode=
Requested by
Host: prra.spxl.socy.es
URL: https://prra.spxl.socy.es/pixel/js/L40P3qKlFpP589/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
178.33.150.172 , France, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
ip172.ip-178-33-150.eu
Software
Microsoft-IIS/7.5 / ASP.NET
Resource Hash
41a24c8fc108a45fab4d2fef4ecc666678cc5f2958664a27ae8aa2fa1d7fa651

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
access-control-expose-headers
Expires,Cache-Control,X-Accel-Expires,Content-Type,Access-Control-Allow-Origin
x-aspnet-version
4.0.30319
content-encoding
gzip
x-backend-addr
10.244.7.176
access-control-allow-methods
GET,POST,HEAD,OPTIONS
expires
Thu, 01 Jan 1970 00:00:00 GMT
access-control-allow-origin
*
date
Thu, 01 Oct 2026 18:57:05 GMT
content-type
application/json
x-powered-by
ASP.NET
server
Microsoft-IIS/7.5
x-accel-expires
0
access-control-allow-headers
DNT,X-CustomHeader,Keep-Alive,User-Agent,X-Requested-With,If-Modified-Since,Cache-Control,Content-Type,Authorization,Referer,Accept
GET
H2
200
RCc4c3550986e94b03a5626310d1b12bd9-source.min.js Show response
assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/
29 KB
8 KB
22ms
22ms
Script
application/x-javascript
2a02:26f0:2780:a9e::1e80
AKAMAI-ASN1 Akama...
General
Full URL
https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/RCc4c3550986e94b03a5626310d1b12bd9-source.min.js
Requested by
Host: assets.adobedtm.com
URL: https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/launch-4756de8c2616.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:2780:a9e::1e80 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
AkamaiNetStorage /
Resource Hash
d231df6f9389398eec75616710dc53dd64315a69dfdfebaaa2cbf0f824a0c456
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=3600
timing-allow-origin
*
content-encoding
gzip
etag
"423ca4e44d5342021fc9d3d04cbea55a:1790086492.212561"
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 19:57:05 GMT
accept-ranges
bytes
access-control-allow-origin
https://los40.com.pa
content-length
8282
date
Thu, 01 Oct 2026 18:57:05 GMT
content-type
application/x-javascript
last-modified
Tue, 22 Sep 2026 14:14:52 GMT
server
AkamaiNetStorage
vary
Accept-Encoding
GET
H3
204
generate_204
www.youtube.com/ Frame CCE2
0
10 B
18ms
18ms
Image
text/plain
142.251.155.119
Google LLC
General
Full URL
https://www.youtube.com/generate_204?aBPeWQ
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.155.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/s3a4OQR-10M
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
0
date
Thu, 01 Oct 2026 18:57:05 GMT
cross-origin-resource-policy
cross-origin
GET
H3
204
generate_204
www.youtube.com/ Frame 8D10
0
10 B
17ms
17ms
Image
text/plain
142.251.155.119
Google LLC
General
Full URL
https://www.youtube.com/generate_204?e-CDBw
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.155.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/fRIhCiUVaKs
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
0
date
Thu, 01 Oct 2026 18:57:05 GMT
cross-origin-resource-policy
cross-origin
GET
H3
204
generate_204
www.youtube.com/ Frame B420
0
10 B
16ms
16ms
Image
text/plain
142.251.155.119
Google LLC
General
Full URL
https://www.youtube.com/generate_204?Dra8bQ
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.155.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/_1W51TfwOEA
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
0
date
Thu, 01 Oct 2026 18:57:05 GMT
cross-origin-resource-policy
cross-origin
GET

getuid
ib.adnxs.com/ Frame 0222
0
0


OPTIONS
H2
200
GenerateIT
jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/ Frame
0
0
85ms
31ms
Preflight
text/html
2001:4860:4841:400::
Google LLC
General
Full URL
https://jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/GenerateIT
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2001:4860:4841:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

Accept
*/*
Access-Control-Request-Headers
content-type,x-goog-api-key
Access-Control-Request-Method
POST
Origin
https://www.youtube.com
Sec-Fetch-Mode
cors
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36

Response headers

access-control-allow-credentials
true
access-control-allow-headers
content-type,x-goog-api-key
access-control-allow-methods
DELETE,GET,HEAD,OPTIONS,PATCH,POST,PUT
access-control-allow-origin
https://www.youtube.com
access-control-max-age
3600
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
0
content-type
text/html
date
Thu, 01 Oct 2026 18:57:06 GMT
server
ESF
vary
origin referer x-origin
x-content-type-options
nosniff
x-frame-options
SAMEORIGIN
x-xss-protection
0
POST
H2
200
GenerateIT Show response
jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/ Frame 8D10
94 B
181 B
44ms
41ms
XHR
application/json+protobuf
2001:4860:4841:400::
Google LLC
General
Full URL
https://jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/GenerateIT
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQADG/d=1/excm=base,root/br=1/rs=AGKMywHPwBmNjDXkqTzY4KDK4LnhoANgJg/m=root,base
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2001:4860:4841:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
25e85111d31c7b43a4c54ef0ae7865aee1adf2908b7522fc90463fc232eb93bf
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

X-Goog-Api-Key
AIzaSyDyT5W0Jh49F30Pqqtyfdf7pDLFKLJoAnw
sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
Content-Type
application/json+protobuf
sec-ch-ua-mobile
?0

Response headers

access-control-expose-headers
vary,vary,vary,content-encoding,date,server,content-length
content-encoding
gzip
access-control-allow-credentials
true
x-content-type-options
nosniff
access-control-allow-origin
https://www.youtube.com
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
114
date
Thu, 01 Oct 2026 18:57:06 GMT
x-xss-protection
0
content-type
application/json+protobuf; charset=UTF-8
vary
Origin, X-Origin, Referer
server
ESF
x-frame-options
SAMEORIGIN
OPTIONS
H2
200
GenerateIT
jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/ Frame
0
0
72ms
33ms
Preflight
text/html
2001:4860:4841:400::
Google LLC
General
Full URL
https://jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/GenerateIT
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2001:4860:4841:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

Accept
*/*
Access-Control-Request-Headers
content-type,x-goog-api-key
Access-Control-Request-Method
POST
Origin
https://www.youtube.com
Sec-Fetch-Mode
cors
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36

Response headers

access-control-allow-credentials
true
access-control-allow-headers
content-type,x-goog-api-key
access-control-allow-methods
DELETE,GET,HEAD,OPTIONS,PATCH,POST,PUT
access-control-allow-origin
https://www.youtube.com
access-control-max-age
3600
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
0
content-type
text/html
date
Thu, 01 Oct 2026 18:57:06 GMT
server
ESF
vary
origin referer x-origin
x-content-type-options
nosniff
x-frame-options
SAMEORIGIN
x-xss-protection
0
POST
H2
200
GenerateIT Show response
jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/ Frame B420
94 B
181 B
42ms
39ms
XHR
application/json+protobuf
2001:4860:4841:400::
Google LLC
General
Full URL
https://jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/GenerateIT
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2001:4860:4841:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
fc8a1209662da01173b39d81a8cbd9c37eee64fd6d927f471006148f0b7dac9a
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

X-Goog-Api-Key
AIzaSyDyT5W0Jh49F30Pqqtyfdf7pDLFKLJoAnw
sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
Content-Type
application/json+protobuf
sec-ch-ua-mobile
?0

Response headers

access-control-expose-headers
vary,vary,vary,content-encoding,date,server,content-length
content-encoding
gzip
access-control-allow-credentials
true
x-content-type-options
nosniff
access-control-allow-origin
https://www.youtube.com
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
114
date
Thu, 01 Oct 2026 18:57:06 GMT
x-xss-protection
0
content-type
application/json+protobuf; charset=UTF-8
vary
Origin, X-Origin, Referer
server
ESF
x-frame-options
SAMEORIGIN
OPTIONS
H2
200
GenerateIT
jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/ Frame
0
0
63ms
32ms
Preflight
text/html
2001:4860:4841:400::
Google LLC
General
Full URL
https://jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/GenerateIT
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2001:4860:4841:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

Accept
*/*
Access-Control-Request-Headers
content-type,x-goog-api-key
Access-Control-Request-Method
POST
Origin
https://www.youtube.com
Sec-Fetch-Mode
cors
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36

Response headers

access-control-allow-credentials
true
access-control-allow-headers
content-type,x-goog-api-key
access-control-allow-methods
DELETE,GET,HEAD,OPTIONS,PATCH,POST,PUT
access-control-allow-origin
https://www.youtube.com
access-control-max-age
3600
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
0
content-type
text/html
date
Thu, 01 Oct 2026 18:57:06 GMT
server
ESF
vary
origin referer x-origin
x-content-type-options
nosniff
x-frame-options
SAMEORIGIN
x-xss-protection
0
POST
H2
200
GenerateIT Show response
jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/ Frame CCE2
94 B
304 B
38ms
35ms
XHR
application/json+protobuf
2001:4860:4841:400::
Google LLC
General
Full URL
https://jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/GenerateIT
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2001:4860:4841:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
5c49f23c1aa61273f0426906fdf87115f14eff7c0e783b44551e9fce03f7431e
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

X-Goog-Api-Key
AIzaSyDyT5W0Jh49F30Pqqtyfdf7pDLFKLJoAnw
sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
Content-Type
application/json+protobuf
sec-ch-ua-mobile
?0

Response headers

access-control-expose-headers
vary,vary,vary,content-encoding,date,server,content-length
content-encoding
gzip
access-control-allow-credentials
true
x-content-type-options
nosniff
access-control-allow-origin
https://www.youtube.com
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
114
date
Thu, 01 Oct 2026 18:57:06 GMT
x-xss-protection
0
content-type
application/json+protobuf; charset=UTF-8
vary
Origin, X-Origin, Referer
server
ESF
x-frame-options
SAMEORIGIN
GET
H2
200
RC2af9221d937e47928f1daec0a7d8beef-source.min.js Show response
assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/
2 KB
1 KB
23ms
23ms
Script
application/x-javascript
2a02:26f0:2780:a9e::1e80
AKAMAI-ASN1 Akama...
General
Full URL
https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/RC2af9221d937e47928f1daec0a7d8beef-source.min.js
Requested by
Host: assets.adobedtm.com
URL: https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/launch-4756de8c2616.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:2780:a9e::1e80 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
AkamaiNetStorage /
Resource Hash
a51d1ed6ffaf3d965e806f7b1ef10a337c4378c7b5f0e3be38b6956b35661c05
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=3600
timing-allow-origin
*
content-encoding
gzip
etag
"423ca4e44d5342021fc9d3d04cbea55a:1790086492.212561"
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 19:57:06 GMT
accept-ranges
bytes
access-control-allow-origin
https://los40.com.pa
content-length
899
date
Thu, 01 Oct 2026 18:57:06 GMT
content-type
application/x-javascript
last-modified
Tue, 22 Sep 2026 14:14:52 GMT
server
AkamaiNetStorage
vary
Accept-Encoding
GET
H2
200
RCe39d3dc701ed4f3da2f60531ada454de-source.min.js Show response
assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/
4 KB
2 KB
23ms
23ms
Script
application/x-javascript
2a02:26f0:2780:a9e::1e80
AKAMAI-ASN1 Akama...
General
Full URL
https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/RCe39d3dc701ed4f3da2f60531ada454de-source.min.js
Requested by
Host: assets.adobedtm.com
URL: https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/launch-4756de8c2616.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:2780:a9e::1e80 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
AkamaiNetStorage /
Resource Hash
d1d39a41576fc9baacb643f6f26beb557215f5d8fd2297171eefc6b3685d1ef7
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=3600
timing-allow-origin
*
content-encoding
gzip
etag
"423ca4e44d5342021fc9d3d04cbea55a:1790086492.212561"
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 19:57:06 GMT
accept-ranges
bytes
access-control-allow-origin
https://los40.com.pa
content-length
1391
date
Thu, 01 Oct 2026 18:57:06 GMT
content-type
application/x-javascript
last-modified
Tue, 22 Sep 2026 14:14:52 GMT
server
AkamaiNetStorage
vary
Accept-Encoding
GET
H2
200
RC75089dd5fb074210bac3f2327428ba58-source.min.js Show response
assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/
14 KB
4 KB
24ms
24ms
Script
application/x-javascript
2a02:26f0:2780:a9e::1e80
AKAMAI-ASN1 Akama...
General
Full URL
https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/RC75089dd5fb074210bac3f2327428ba58-source.min.js
Requested by
Host: assets.adobedtm.com
URL: https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/launch-4756de8c2616.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:2780:a9e::1e80 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
AkamaiNetStorage /
Resource Hash
00e0c89c0f922c98de0de5d4b3f359ca5995a269f8d74831f6ecb79d6ef1b916
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=3600
timing-allow-origin
*
content-encoding
gzip
etag
"423ca4e44d5342021fc9d3d04cbea55a:1790086492.212561"
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 19:57:06 GMT
accept-ranges
bytes
access-control-allow-origin
https://los40.com.pa
content-length
3690
date
Thu, 01 Oct 2026 18:57:06 GMT
content-type
application/x-javascript
last-modified
Tue, 22 Sep 2026 14:14:52 GMT
server
AkamaiNetStorage
vary
Accept-Encoding
GET
H2
200
RC6ab26925b4e942d7a9648d84988933a6-source.min.js Show response
assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/
2 KB
1 KB
23ms
23ms
Script
application/x-javascript
2a02:26f0:2780:a9e::1e80
AKAMAI-ASN1 Akama...
General
Full URL
https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/RC6ab26925b4e942d7a9648d84988933a6-source.min.js
Requested by
Host: assets.adobedtm.com
URL: https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/launch-4756de8c2616.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:2780:a9e::1e80 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
AkamaiNetStorage /
Resource Hash
00f5a7dd994f87d2312bafc45ea100e7901d6259aac1858b1d7eaaa069e7ea1e
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=3600
timing-allow-origin
*
content-encoding
gzip
etag
"423ca4e44d5342021fc9d3d04cbea55a:1790086492.212561"
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 19:57:06 GMT
accept-ranges
bytes
access-control-allow-origin
https://los40.com.pa
content-length
857
date
Thu, 01 Oct 2026 18:57:06 GMT
content-type
application/x-javascript
last-modified
Tue, 22 Sep 2026 14:14:52 GMT
server
AkamaiNetStorage
vary
Accept-Encoding
GET
H2
200
RC07375797c6b648b6b9a5c86ad0465041-source.min.js Show response
assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/
4 KB
2 KB
23ms
23ms
Script
application/x-javascript
2a02:26f0:2780:a9e::1e80
AKAMAI-ASN1 Akama...
General
Full URL
https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/RC07375797c6b648b6b9a5c86ad0465041-source.min.js
Requested by
Host: assets.adobedtm.com
URL: https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/launch-4756de8c2616.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:2780:a9e::1e80 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
AkamaiNetStorage /
Resource Hash
5cbb53b20b48230acf93104dfb18edcce5abeb39cf59999c1b8910d2c3f23142
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=3600
timing-allow-origin
*
content-encoding
gzip
etag
"423ca4e44d5342021fc9d3d04cbea55a:1790086492.212561"
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 19:57:06 GMT
accept-ranges
bytes
access-control-allow-origin
https://los40.com.pa
content-length
1463
date
Thu, 01 Oct 2026 18:57:06 GMT
content-type
application/x-javascript
last-modified
Tue, 22 Sep 2026 14:14:52 GMT
server
AkamaiNetStorage
vary
Accept-Encoding
GET
H2
200
RCe36344e51da54343a37c576e0815fc36-source.min.js Show response
assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/
1 KB
1010 B
23ms
23ms
Script
application/x-javascript
2a02:26f0:2780:a9e::1e80
AKAMAI-ASN1 Akama...
General
Full URL
https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/RCe36344e51da54343a37c576e0815fc36-source.min.js
Requested by
Host: assets.adobedtm.com
URL: https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/launch-4756de8c2616.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:2780:a9e::1e80 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
AkamaiNetStorage /
Resource Hash
ecd3bcd411bcfdc529beaa8281bb796f35572e3a3b6329cf34717f886fab9efc
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=3600
timing-allow-origin
*
content-encoding
gzip
etag
"423ca4e44d5342021fc9d3d04cbea55a:1790086492.212561"
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 19:57:06 GMT
accept-ranges
bytes
access-control-allow-origin
https://los40.com.pa
content-length
733
date
Thu, 01 Oct 2026 18:57:06 GMT
content-type
application/x-javascript
last-modified
Tue, 22 Sep 2026 14:14:52 GMT
server
AkamaiNetStorage
vary
Accept-Encoding
GET
H2
200
RC6dac717d64f74222b45039c65b0d9d1b-source.min.js Show response
assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/
671 B
625 B
29ms
29ms
Script
application/x-javascript
2a02:26f0:2780:a9e::1e80
AKAMAI-ASN1 Akama...
General
Full URL
https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/RC6dac717d64f74222b45039c65b0d9d1b-source.min.js
Requested by
Host: assets.adobedtm.com
URL: https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/launch-4756de8c2616.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:2780:a9e::1e80 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
AkamaiNetStorage /
Resource Hash
a48033ab8dbf9f974469ec1285b2317c398a9250a4d0467e3ac7e993a055b157
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=3600
timing-allow-origin
*
content-encoding
gzip
etag
"423ca4e44d5342021fc9d3d04cbea55a:1790086492.212561"
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 19:57:06 GMT
accept-ranges
bytes
access-control-allow-origin
https://los40.com.pa
content-length
348
date
Thu, 01 Oct 2026 18:57:06 GMT
content-type
application/x-javascript
last-modified
Tue, 22 Sep 2026 14:14:52 GMT
server
AkamaiNetStorage
vary
Accept-Encoding
GET
H2
200
RC091f762293c24eaebe3bf4a0560242dd-source.min.js Show response
assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/
1 KB
1022 B
29ms
28ms
Script
application/x-javascript
2a02:26f0:2780:a9e::1e80
AKAMAI-ASN1 Akama...
General
Full URL
https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/RC091f762293c24eaebe3bf4a0560242dd-source.min.js
Requested by
Host: assets.adobedtm.com
URL: https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/launch-4756de8c2616.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:2780:a9e::1e80 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
AkamaiNetStorage /
Resource Hash
cf0423cf281ce89ea32e234549d2055f6c19b0d982aa3f8c3b147070f49e24fd
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=3600
timing-allow-origin
*
content-encoding
gzip
etag
"423ca4e44d5342021fc9d3d04cbea55a:1790086492.212561"
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 19:57:06 GMT
accept-ranges
bytes
access-control-allow-origin
https://los40.com.pa
content-length
745
date
Thu, 01 Oct 2026 18:57:06 GMT
content-type
application/x-javascript
last-modified
Tue, 22 Sep 2026 14:14:52 GMT
server
AkamaiNetStorage
vary
Accept-Encoding
GET
H2
200
RC1e262c30b2284ae29250b0a6b8902f5e-source.min.js Show response
assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/
593 B
637 B
28ms
28ms
Script
application/x-javascript
2a02:26f0:2780:a9e::1e80
AKAMAI-ASN1 Akama...
General
Full URL
https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/RC1e262c30b2284ae29250b0a6b8902f5e-source.min.js
Requested by
Host: assets.adobedtm.com
URL: https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/launch-4756de8c2616.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:2780:a9e::1e80 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
AkamaiNetStorage /
Resource Hash
5feb6ccd9965ded425e1e8d2bd1797ab9740d592d47f23cb84740dc8169d58ee
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=3600
timing-allow-origin
*
content-encoding
gzip
etag
"423ca4e44d5342021fc9d3d04cbea55a:1790086492.212561"
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 19:57:06 GMT
accept-ranges
bytes
access-control-allow-origin
https://los40.com.pa
content-length
360
date
Thu, 01 Oct 2026 18:57:06 GMT
content-type
application/x-javascript
last-modified
Tue, 22 Sep 2026 14:14:52 GMT
server
AkamaiNetStorage
vary
Accept-Encoding
GET
H2
200
RCb0816929e29942b4a6314646a8980409-source.min.js Show response
assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/
4 KB
2 KB
28ms
28ms
Script
application/x-javascript
2a02:26f0:2780:a9e::1e80
AKAMAI-ASN1 Akama...
General
Full URL
https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/RCb0816929e29942b4a6314646a8980409-source.min.js
Requested by
Host: assets.adobedtm.com
URL: https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/launch-4756de8c2616.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:2780:a9e::1e80 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
AkamaiNetStorage /
Resource Hash
d4541ccc650611057ee03ca66fe00a75120ccb64b539302b772c7753c1ce6675
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=3600
timing-allow-origin
*
content-encoding
gzip
etag
"423ca4e44d5342021fc9d3d04cbea55a:1790086492.212561"
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 19:57:06 GMT
accept-ranges
bytes
access-control-allow-origin
https://los40.com.pa
content-length
1615
date
Thu, 01 Oct 2026 18:57:06 GMT
content-type
application/x-javascript
last-modified
Tue, 22 Sep 2026 14:14:52 GMT
server
AkamaiNetStorage
vary
Accept-Encoding
GET
H2
200
RC11ac54382a244bcb9b9c1139990d2818-source.min.js Show response
assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/
687 B
632 B
42ms
42ms
Script
application/x-javascript
2a02:26f0:2780:a9e::1e80
AKAMAI-ASN1 Akama...
General
Full URL
https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/RC11ac54382a244bcb9b9c1139990d2818-source.min.js
Requested by
Host: assets.adobedtm.com
URL: https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/launch-4756de8c2616.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:2780:a9e::1e80 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
AkamaiNetStorage /
Resource Hash
62f672d6a1e7408e0d1806bc80ced1f939c4bd054d0d8216f4842c15c16bb01d
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=3600
timing-allow-origin
*
content-encoding
gzip
etag
"423ca4e44d5342021fc9d3d04cbea55a:1790086492.212561"
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 19:57:06 GMT
accept-ranges
bytes
access-control-allow-origin
https://los40.com.pa
content-length
355
date
Thu, 01 Oct 2026 18:57:06 GMT
content-type
application/x-javascript
last-modified
Tue, 22 Sep 2026 14:14:52 GMT
server
AkamaiNetStorage
vary
Accept-Encoding
GET
H2
200
RC42fef2d950354e96944c9b65b5dc91ff-source.min.js Show response
assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/
3 KB
1 KB
42ms
41ms
Script
application/x-javascript
2a02:26f0:2780:a9e::1e80
AKAMAI-ASN1 Akama...
General
Full URL
https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/RC42fef2d950354e96944c9b65b5dc91ff-source.min.js
Requested by
Host: assets.adobedtm.com
URL: https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/launch-4756de8c2616.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:2780:a9e::1e80 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
AkamaiNetStorage /
Resource Hash
d2ec536529cfefef0eab6453e615717281a7a52ab0a099767315b87c441f9ef5
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=3600
timing-allow-origin
*
content-encoding
gzip
etag
"423ca4e44d5342021fc9d3d04cbea55a:1790086492.212561"
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 19:57:06 GMT
accept-ranges
bytes
access-control-allow-origin
https://los40.com.pa
content-length
1013
date
Thu, 01 Oct 2026 18:57:06 GMT
content-type
application/x-javascript
last-modified
Tue, 22 Sep 2026 14:14:52 GMT
server
AkamaiNetStorage
vary
Accept-Encoding
GET
H2
200
RC6ec0831553b44494bba89ae9e9411c88-source.min.js Show response
assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/
351 B
501 B
42ms
41ms
Script
application/x-javascript
2a02:26f0:2780:a9e::1e80
AKAMAI-ASN1 Akama...
General
Full URL
https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/RC6ec0831553b44494bba89ae9e9411c88-source.min.js
Requested by
Host: assets.adobedtm.com
URL: https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/launch-4756de8c2616.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:2780:a9e::1e80 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
AkamaiNetStorage /
Resource Hash
ff40dc96cdd64de6e3890158055fff059e9e6256bdc0c4be719ad1e079bcdb4d
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=3600
timing-allow-origin
*
content-encoding
gzip
etag
"423ca4e44d5342021fc9d3d04cbea55a:1790086492.212561"
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 19:57:06 GMT
accept-ranges
bytes
access-control-allow-origin
https://los40.com.pa
content-length
225
date
Thu, 01 Oct 2026 18:57:06 GMT
content-type
application/x-javascript
last-modified
Tue, 22 Sep 2026 14:14:52 GMT
server
AkamaiNetStorage
vary
Accept-Encoding
GET
H2
200
RCd3306e5701b741b4aa625ed4239e1c4d-source.min.js Show response
assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/
1 KB
875 B
42ms
41ms
Script
application/x-javascript
2a02:26f0:2780:a9e::1e80
AKAMAI-ASN1 Akama...
General
Full URL
https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/RCd3306e5701b741b4aa625ed4239e1c4d-source.min.js
Requested by
Host: assets.adobedtm.com
URL: https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/launch-4756de8c2616.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:2780:a9e::1e80 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
AkamaiNetStorage /
Resource Hash
feb61f57061c97d1a775d1aee86665ae9d3a705c9a384da8980829450e8a4260
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=3600
timing-allow-origin
*
content-encoding
gzip
etag
"423ca4e44d5342021fc9d3d04cbea55a:1790086492.212561"
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 19:57:06 GMT
accept-ranges
bytes
access-control-allow-origin
https://los40.com.pa
content-length
598
date
Thu, 01 Oct 2026 18:57:06 GMT
content-type
application/x-javascript
last-modified
Tue, 22 Sep 2026 14:14:52 GMT
server
AkamaiNetStorage
vary
Accept-Encoding
GET
H2
200
RC4216d03233c840d390bd0935aa2eb0e1-source.min.js Show response
assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/
612 B
621 B
42ms
42ms
Script
application/x-javascript
2a02:26f0:2780:a9e::1e80
AKAMAI-ASN1 Akama...
General
Full URL
https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/RC4216d03233c840d390bd0935aa2eb0e1-source.min.js
Requested by
Host: assets.adobedtm.com
URL: https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/launch-4756de8c2616.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:2780:a9e::1e80 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
AkamaiNetStorage /
Resource Hash
896b02fd97d42f7620cd2c9e5fc1b16c64b447469fd6df06747bf283028e7784
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=3600
timing-allow-origin
*
content-encoding
gzip
etag
"423ca4e44d5342021fc9d3d04cbea55a:1790086492.212561"
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 19:57:06 GMT
accept-ranges
bytes
access-control-allow-origin
https://los40.com.pa
content-length
344
date
Thu, 01 Oct 2026 18:57:06 GMT
content-type
application/x-javascript
last-modified
Tue, 22 Sep 2026 14:14:52 GMT
server
AkamaiNetStorage
vary
Accept-Encoding
GET
H2
200
RC9bd94b721c274a4bb374d6f1a510fb30-source.min.js Show response
assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/
451 B
545 B
42ms
42ms
Script
application/x-javascript
2a02:26f0:2780:a9e::1e80
AKAMAI-ASN1 Akama...
General
Full URL
https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/782617660794/RC9bd94b721c274a4bb374d6f1a510fb30-source.min.js
Requested by
Host: assets.adobedtm.com
URL: https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/launch-4756de8c2616.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:2780:a9e::1e80 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
AkamaiNetStorage /
Resource Hash
657aaec2cfe6fc02cbdf55326617378d9b813702d4fe6d1d330e7d92ee4450ac
Security Headers
Name Value
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=3600
timing-allow-origin
*
content-encoding
gzip
etag
"423ca4e44d5342021fc9d3d04cbea55a:1790086492.212561"
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 19:57:06 GMT
accept-ranges
bytes
access-control-allow-origin
https://los40.com.pa
content-length
268
date
Thu, 01 Oct 2026 18:57:06 GMT
content-type
application/x-javascript
last-modified
Tue, 22 Sep 2026 14:14:52 GMT
server
AkamaiNetStorage
vary
Accept-Encoding
GET
H3
200
src_sdk_core_modules_integrations_sdk-integrations_providers_google_google_js.2af281429ae434027f53ac77f93097d5b4488b76.js Show response
sdk.privacy-center.org/sdk/2af281429ae434027f53ac77f93097d5b4488b76/modern/
2 KB
1 KB
25ms
25ms
Script
application/javascript
3.174.46.14
Amazon.com
General
Full URL
https://sdk.privacy-center.org/sdk/2af281429ae434027f53ac77f93097d5b4488b76/modern/src_sdk_core_modules_integrations_sdk-integrations_providers_google_google_js.2af281429ae434027f53ac77f93097d5b4488b76.js
Requested by
Host: sdk.privacy-center.org
URL: https://sdk.privacy-center.org/sdk/2af281429ae434027f53ac77f93097d5b4488b76/modern/sdk.2af281429ae434027f53ac77f93097d5b4488b76.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
3.174.46.14 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-174-46-14.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
eb47d1409ae84e69d57499f00ed9b17fed8549ae4a1cf508385037a15adfa6ca

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
cache-control
public, max-age=31536000
content-encoding
br
etag
W/"0d1fb5fcb4bc7bed9aa26ce8fafbb12d-1"
age
104517
via
1.1 278fc31388a17e0af9d84be18de80a5a.cloudfront.net (CloudFront)
alt-svc
h3=":443"; ma=86400
x-cache
Hit from cloudfront
x-amz-cf-id
_ZrKD0iLtE3SpYnnQx9BDBoUf_R2LmsGzcSsPaR0kq-hxbFMkUHQCQ==
date
Wed, 30 Sep 2026 13:55:10 GMT
content-type
application/javascript; charset=utf-8
last-modified
Wed, 30 Sep 2026 13:55:01 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P12
x-amz-server-side-encryption
AES256
GET
H3
200
src_sdk_core_modules_integrations_sdk-integrations_providers_gcm_gcm_js.2af281429ae434027f53ac77f93097d5b4488b76.js Show response
sdk.privacy-center.org/sdk/2af281429ae434027f53ac77f93097d5b4488b76/modern/
3 KB
1 KB
26ms
26ms
Script
application/javascript
3.174.46.14
Amazon.com
General
Full URL
https://sdk.privacy-center.org/sdk/2af281429ae434027f53ac77f93097d5b4488b76/modern/src_sdk_core_modules_integrations_sdk-integrations_providers_gcm_gcm_js.2af281429ae434027f53ac77f93097d5b4488b76.js
Requested by
Host: sdk.privacy-center.org
URL: https://sdk.privacy-center.org/sdk/2af281429ae434027f53ac77f93097d5b4488b76/modern/sdk.2af281429ae434027f53ac77f93097d5b4488b76.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
3.174.46.14 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-174-46-14.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
cc730a79aad4de1ffe9b8ab9fa59daeed7c82ad02a3cc54a4c692a0243a488af

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
cache-control
public, max-age=31536000
content-encoding
br
etag
W/"7bc705b831f0fe8a9782f6127f8a2c36-1"
age
104511
via
1.1 278fc31388a17e0af9d84be18de80a5a.cloudfront.net (CloudFront)
alt-svc
h3=":443"; ma=86400
x-cache
Hit from cloudfront
x-amz-cf-id
01pzctUzxKx8oVbinfxqNAxy_mheBpoVIk3pQ_U6g_k59wnlTqStWw==
date
Wed, 30 Sep 2026 13:55:16 GMT
content-type
application/javascript; charset=utf-8
last-modified
Wed, 30 Sep 2026 13:55:01 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P12
x-amz-server-side-encryption
AES256
GET
H2
200
ibs:dpid=771&dpuuid=CAESEPNJjf-6UxETQKeV303PRbM&google_cver=1
dpm.demdex.net/ Frame 0222
Redirect Chain
  • https://cm.g.doubleclick.net/pixel?google_nid=adobe_dmp&google_cm&gdpr=0&gdpr_consent=&google_hm=NzA2MTUwMTUxODUzMDgxMTYxNjI3MDUyNTc0Mzg4NzEzNjA4NDE=
  • https://cm.g.doubleclick.net/pixel?google_nid=adobe_dmp&google_cm=&gdpr=0&gdpr_consent=&google_hm=NzA2MTUwMTUxODUzMDgxMTYxNjI3MDUyNTc0Mzg4NzEzNjA4NDE=&google_tc=
  • https://dpm.demdex.net/ibs:dpid=771&dpuuid=CAESEPNJjf-6UxETQKeV303PRbM&google_cver=1?gdpr=0&gdpr_consent=
42 B
704 B
51ms
50ms
Image
image/gif
52.17.233.147
Amazon.com
General
Full URL
https://dpm.demdex.net/ibs:dpid=771&dpuuid=CAESEPNJjf-6UxETQKeV303PRbM&google_cver=1?gdpr=0&gdpr_consent=
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Server
52.17.233.147 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-52-17-233-147.eu-west-1.compute.amazonaws.com
Software
/
Resource Hash
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Content-Type-Options nosniff

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
Referer
https://prisacom.demdex.net/

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
no-cache,no-store,must-revalidate,max-age=0,proxy-revalidate,no-transform,private
dcs
dcs-prod-irl1-2-v097-0e66c190e.edge-irl1.demdex.com 6 ms
content-encoding
zstd
pragma
no-cache
x-content-type-options
nosniff
x-tid
+UXbcM+1MCQ=
expires
Thu, 01 Jan 1970 00:00:00 UTC
content-length
46
p3p
policyref="/w3c/p3p.xml", CP="NOI NID CURa ADMa DEVa PSAa PSDa OUR SAMa BUS PUR COM NAV INT"
date
Thu, 01 Oct 2026 18:57:06 GMT
content-type
image/gif

Redirect headers

cache-control
no-cache, must-revalidate
location
https://dpm.demdex.net/ibs:dpid=771&dpuuid=CAESEPNJjf-6UxETQKeV303PRbM&google_cver=1?gdpr=0&gdpr_consent=
pragma
no-cache
cross-origin-resource-policy
cross-origin
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
content-length
314
date
Thu, 01 Oct 2026 18:57:06 GMT
x-xss-protection
0
content-type
text/html; charset=UTF-8
server
HTTP server (unknown)
POST
H2
200
acquire Show response
adobedc.demdex.net/ee/v1/identity/
824 B
989 B
126ms
54ms
Fetch
application/json
63.140.62.210
Amazon.com
General
Full URL
https://adobedc.demdex.net/ee/v1/identity/acquire?configId=9ad480a3-985a-4cc5-9907-d80eae43012e&requestId=8ceaae8d-dd1f-439c-8e10-dea4258952e3
Requested by
Host: assets.adobedtm.com
URL: https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/launch-4756de8c2616.min.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
63.140.62.210 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ip-63-140-62-210.data.adobedc.net
Software
jag /
Resource Hash
31b2631f7b0931b746105ed464b2469bae130674907729c58554d4e9b259847c
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
Content-Type
text/plain; charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
x-request-id
8ceaae8d-dd1f-439c-8e10-dea4258952e3-1fad5ce2ca0041cd
access-control-expose-headers
Retry-After, X-Adobe-Edge, X-Request-ID
cache-control
no-cache, no-store, max-age=0, no-transform, private
content-encoding
gzip
x-adobe-edge
IRL1;6
access-control-allow-credentials
true
x-content-type-options
nosniff
access-control-allow-origin
https://los40.com.pa
date
Thu, 01 Oct 2026 18:57:06 GMT
x-xss-protection
1; mode=block
x-konductor
26.9.5-HEAD-SNAPSHOT:f5db96293
vary
Origin
server
jag
content-type
application/json;charset=utf-8
GET
H2
200
iframe_api Show response
www.youtube.com/
993 B
3 KB
110ms
64ms
Script
text/javascript
2001:4860:482b:400::
Google LLC
General
Full URL
https://www.youtube.com/iframe_api
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:482b:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
248cc827d02e70984c52df2fa3f261eca39f6d3c0a8a24a37f4a407ee4d8d337
Security Headers
Name Value
Content-Security-Policy script-src 'unsafe-eval' 'self' 'unsafe-inline' https://www.google.com https://apis.google.com https://ssl.gstatic.com https://www.gstatic.com https://www.googletagmanager.com https://www.google-analytics.com https://*.youtube.com https://*.google.com https://*.gstatic.com https://youtube.com https://www.youtube.com https://google.com https://*.doubleclick.net https://*.googleapis.com https://www.googleadservices.com https://tpc.googlesyndication.com https://www.youtubekids.com https://www.youtube-nocookie.com https://www.youtubeeducation.com https://www-onepick-opensocial.googleusercontent.com;report-uri https://csp.withgoogle.com/csp/youtube_main/allowlist, base-uri 'self';object-src 'none';script-src 'report-sample' 'nonce-4Ns8cwF-bt3mqfgP8j7xPw' 'unsafe-inline' 'strict-dynamic' https: http: 'unsafe-eval';report-uri https://csp.withgoogle.com/csp/youtube_main/strict, require-trusted-types-for 'script'
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
report-to
{"group":"youtube_main","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube_main"}]}
x-content-type-options
nosniff
origin-trial
AmhMBR6zCLzDDxpW+HfpP67BqwIknWnyMOXOQGfzYswFmJe+fgaI6XZgAzcxOrzNtP7hEDsOo1jdjFnVr2IdxQ4AAAB4eyJvcmlnaW4iOiJodHRwczovL3lvdXR1YmUuY29tOjQ0MyIsImZlYXR1cmUiOiJXZWJWaWV3WFJlcXVlc3RlZFdpdGhEZXByZWNhdGlvbiIsImV4cGlyeSI6MTc1ODA2NzE5OSwiaXNTdWJkb21haW4iOnRydWV9, AiDEBptUfVeO93q48VdVMe/ubupazdAl8AaHP+NBzdnW8quUcHdzJUyGSfrmtpKJu7EOvwRp9ug2rEo3XU+WMAMAAAB2eyJvcmlnaW4iOiJodHRwczovL3lvdXR1YmUuY29tOjQ0MyIsImZlYXR1cmUiOiJEZXZpY2VCb3VuZFNlc3Npb25DcmVkZW50aWFsczIiLCJleHBpcnkiOjE3NzQzMTA0MDAsImlzU3ViZG9tYWluIjp0cnVlfQ==
expires
Thu, 01 Oct 2026 18:57:06 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
CP="This is not a P3P policy! See http://support.google.com/accounts/answer/151657?hl=de for more info."
date
Thu, 01 Oct 2026 18:57:06 GMT
content-type
text/javascript; charset=utf-8
vary
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=31536000
content-security-policy
script-src 'unsafe-eval' 'self' 'unsafe-inline' https://www.google.com https://apis.google.com https://ssl.gstatic.com https://www.gstatic.com https://www.googletagmanager.com https://www.google-analytics.com https://*.youtube.com https://*.google.com https://*.gstatic.com https://youtube.com https://www.youtube.com https://google.com https://*.doubleclick.net https://*.googleapis.com https://www.googleadservices.com https://tpc.googlesyndication.com https://www.youtubekids.com https://www.youtube-nocookie.com https://www.youtubeeducation.com https://www-onepick-opensocial.googleusercontent.com;report-uri https://csp.withgoogle.com/csp/youtube_main/allowlist, base-uri 'self';object-src 'none';script-src 'report-sample' 'nonce-4Ns8cwF-bt3mqfgP8j7xPw' 'unsafe-inline' 'strict-dynamic' https: http: 'unsafe-eval';report-uri https://csp.withgoogle.com/csp/youtube_main/strict, require-trusted-types-for 'script'
cache-control
private, max-age=0
accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
cross-origin-resource-policy
cross-origin
permissions-policy
ch-ua-arch=*, ch-ua-bitness=*, ch-ua-full-version=*, ch-ua-full-version-list=*, ch-ua-model=*, ch-ua-wow64=*, ch-ua-form-factors=*, ch-ua-platform=*, ch-ua-platform-version=*
cross-origin-opener-policy-report-only
same-origin; report-to="youtube_main"
x-xss-protection
0
server
ESF
GET
H/1.1
400
Bad Request
idsync.js
playerservices.live.streamtheworld.com/api/
Redirect Chain
  • https://playerservices.live.streamtheworld.com/api/idsync.js?stationId=&gdpr=0&gdpr_consent=undefined
  • https://playerservices.live.streamtheworld.com/api/idsync.js?stationId=&gdpr=0&gdpr_consent=undefined&bounce=true
0
0
110ms
37ms
Script
application/javascript
192.173.31.109
Triton Digital
General
Full URL
https://playerservices.live.streamtheworld.com/api/idsync.js?stationId=&gdpr=0&gdpr_consent=undefined&bounce=true
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
HTTP/1.1
Server
192.173.31.109 , Canada, ASN13360 (TRITONDIGITAL - Triton Digital, CA),
Reverse DNS
Software
/
Resource Hash

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
Referer
https://los40.com.pa/

Response headers

access-control-allow-origin
*
p3p
policyref="http://tds.media.streamtheworld.com/w3c/policy/tds-p3p.xml", CP="NOI DSP COR ADM PSAo PSDo OURo SAMo UNRo OTRo BUS COM NAV DEM STA PRE"
date
Thu, 01 Oct 2026 18:57:06 GMT
x-stw-site
PAR
content-type
application/javascript; charset=ISO-8859-1
connection
close
access-control-allow-credentials
true

Redirect headers

location
https://playerservices.live.streamtheworld.com/api/idsync.js?stationId=&gdpr=0&gdpr_consent=undefined&bounce=true
x-stw-site
PAR
connection
close
access-control-allow-credentials
true
access-control-allow-origin
*
p3p
policyref="http://tds.media.streamtheworld.com/w3c/policy/tds-p3p.xml", CP="NOI DSP COR ADM PSAo PSDo OURo SAMo UNRo OTRo BUS COM NAV DEM STA PRE"
date
Thu, 01 Oct 2026 18:57:06 GMT
content-type
application/javascript; charset=ISO-8859-1
content-language
de-CH
POST
H2
204
delivery
prisacom.tt.omtrdc.net/rest/v1/
0
121 B
53ms
52ms
Ping
text/plain
63.140.62.200
Amazon.com
General
Full URL
https://prisacom.tt.omtrdc.net/rest/v1/delivery?client=prisacom&sessionId=8cf22a303489402fa3d06cfa2438692f&version=2.11.4
Requested by
Host: assets.adobedtm.com
URL: https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/launch-4756de8c2616.min.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
63.140.62.200 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ip-63-140-62-200.data.adobedc.net
Software
jag /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
x-request-id
2be65438-27e2-4a15-b584-e2b437455031
cache-control
no-cache, no-store, max-age=0, no-transform, private
access-control-allow-credentials
true
referrer-policy
strict-origin-when-cross-origin
x-content-type-options
nosniff
access-control-allow-origin
https://los40.com.pa
date
Thu, 01 Oct 2026 18:57:06 GMT
x-xss-protection
1; mode=block
vary
Origin,Access-Control-Request-Method,Access-Control-Request-Headers
server
jag
GET
H2
200
apstag.js Show response
c.amazon-adsystem.com/aax2/
364 KB
93 KB
117ms
39ms
Script
application/javascript
3.173.128.89
Amazon.com
General
Full URL
https://c.amazon-adsystem.com/aax2/apstag.js
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.173.128.89 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-173-128-89.ams56.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
16be8fac20dcb1b8cf7e819d449cc10adb5b9919eaacb5d68c019536aec55648

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
cache-control
max-age=3600
content-encoding
gzip
etag
W/"6da54f52ddb221a65e19eafa7e5f6fe4"
age
2602
via
1.1 a6a96f99e311fd858031f2643574b448.cloudfront.net (CloudFront), 1.1 094c057a1a1a6de6fdb285ef6f030916.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
M-iuhJ_FrpMxuoNxmWmKSF_cGZVZlQeDKbGrD2Bm2M4LwgNbCxVIjw==
date
Thu, 01 Oct 2026 18:13:45 GMT
content-type
application/javascript
x-amz-cf-pop
FRA56-P14, AMS56-P1
server
AmazonS3
last-modified
Thu, 24 Sep 2026 17:57:47 GMT
x-amz-server-side-encryption
AES256
POST
H2
204
delivery
prisacom.tt.omtrdc.net/rest/v1/
0
48 B
51ms
50ms
Ping
text/plain
63.140.62.200
Amazon.com
General
Full URL
https://prisacom.tt.omtrdc.net/rest/v1/delivery?client=prisacom&sessionId=8cf22a303489402fa3d06cfa2438692f&version=2.11.4
Requested by
Host: assets.adobedtm.com
URL: https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/launch-4756de8c2616.min.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
63.140.62.200 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ip-63-140-62-200.data.adobedc.net
Software
jag /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
x-request-id
564fcc1e-ae46-48bd-bb03-27bfb61b2835
cache-control
no-cache, no-store, max-age=0, no-transform, private
access-control-allow-credentials
true
referrer-policy
strict-origin-when-cross-origin
x-content-type-options
nosniff
access-control-allow-origin
https://los40.com.pa
date
Thu, 01 Oct 2026 18:57:06 GMT
x-xss-protection
1; mode=block
vary
Origin,Access-Control-Request-Method,Access-Control-Request-Headers
server
jag
POST
H2
204
delivery
prisacom.tt.omtrdc.net/rest/v1/
0
48 B
54ms
53ms
Ping
text/plain
63.140.62.200
Amazon.com
General
Full URL
https://prisacom.tt.omtrdc.net/rest/v1/delivery?client=prisacom&sessionId=8cf22a303489402fa3d06cfa2438692f&version=2.11.4
Requested by
Host: assets.adobedtm.com
URL: https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/launch-4756de8c2616.min.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
63.140.62.200 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ip-63-140-62-200.data.adobedc.net
Software
jag /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
x-request-id
4c693044-b379-4a09-8b8b-d31cba1a222e
cache-control
no-cache, no-store, max-age=0, no-transform, private
access-control-allow-credentials
true
referrer-policy
strict-origin-when-cross-origin
x-content-type-options
nosniff
access-control-allow-origin
https://los40.com.pa
date
Thu, 01 Oct 2026 18:57:06 GMT
x-xss-protection
1; mode=block
vary
Origin,Access-Control-Request-Method,Access-Control-Request-Headers
server
jag
OPTIONS
H2
200
e571fc265fac50018a554f5329fd64e442c402492069befe67bd5410c95afea7
dcs.adobedc.net/collection/ Frame
0
0
176ms
34ms
Preflight
51.138.12.100
Microsoft Corpora...
General
Full URL
https://dcs.adobedc.net/collection/e571fc265fac50018a554f5329fd64e442c402492069befe67bd5410c95afea7
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
51.138.12.100 Amsterdam, Netherlands, ASN8075 (MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation, US),
Reverse DNS
Software
adobe /
Resource Hash

Request headers

Accept
*/*
Access-Control-Request-Headers
content-type
Access-Control-Request-Method
POST
Origin
https://los40.com.pa
Sec-Fetch-Mode
cors
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36

Response headers

access-control-allow-credentials
true
access-control-allow-headers
Content-Type, content-type
access-control-allow-origin
https://los40.com.pa
access-control-max-age
86400
content-length
0
date
Thu, 01 Oct 2026 18:57:05 GMT
server
adobe
vary
Origin
x-request-id
a5eedf06-6d67-4e80-938b-c36bfc7bf67d
POST
H2
200
e571fc265fac50018a554f5329fd64e442c402492069befe67bd5410c95afea7 Show response
dcs.adobedc.net/collection/
208 B
406 B
38ms
36ms
Fetch
application/json
51.138.12.100
Microsoft Corpora...
General
Full URL
https://dcs.adobedc.net/collection/e571fc265fac50018a554f5329fd64e442c402492069befe67bd5410c95afea7
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
51.138.12.100 Amsterdam, Netherlands, ASN8075 (MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation, US),
Reverse DNS
Software
adobe /
Resource Hash
6ee0adbb8e4fb539be973f11b0c979bbb3e19f1e21bbb84df5e54a9760973e20
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
Accept
application/json
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
Content-Type
application/json
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
x-streaming-ingest
26.9.5-HEAD-SNAPSHOT:f5db96293
x-request-id
3428d714-f399-4a1d-a7ef-3306eec5b42c
access-control-expose-headers
Retry-After, X-Adobe-Edge, X-Request-ID
content-encoding
gzip
x-adobe-edge
VA6;7
access-control-allow-credentials
true
access-control-allow-origin
https://los40.com.pa
date
Thu, 01 Oct 2026 18:57:05 GMT
content-type
application/json;charset=utf-8
vary
Origin
server
adobe
GET
H2
200
perm_musicales.min.js Show response
player.prisamedia.com/core//skins/perm_musicales/
55 KB
14 KB
30ms
29ms
Script
application/javascript
199.232.198.133
Fastly
General
Full URL
https://player.prisamedia.com/core//skins/perm_musicales/perm_musicales.min.js
Requested by
Host: player.prisamedia.com
URL: https://player.prisamedia.com/core//js/coreplayer.min.js
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
199.232.198.133 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
/
Resource Hash
005bf06762a807e300c8a79da4100f20f6184910b22f1d702aafc112efb4bb77

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
"d4fb6f9da1303b903f7c98e967cd7dc9"
age
22095
x-timer
S1790881026.127487,VS0,VE5
via
1.1 varnish
accept-ranges
bytes
access-control-allow-origin
*
x-cache
HIT
content-length
13777
date
Thu, 01 Oct 2026 18:57:06 GMT
last-modified
Thu, 01 Oct 2026 12:36:34 GMT
content-type
application/javascript; charset=utf-8
x-served-by
cache-lin1730051-LIN
x-cache-hits
0
vary
Accept-Encoding
GET
H2
200
td-sdk.min.js Show response
sdk.listenlive.co/web/2.9/
1 MB
364 KB
414ms
322ms
Script
text/javascript
2600:9000:20ab:ea00:1:ef39:a380:93a1
Amazon.com
General
Full URL
https://sdk.listenlive.co/web/2.9/td-sdk.min.js
Requested by
Host: player.prisamedia.com
URL: https://player.prisamedia.com/core//js/coreplayer.min.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2600:9000:20ab:ea00:1:ef39:a380:93a1 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
Software
AmazonS3 /
Resource Hash
f07f071b0126a21c1b964a9bae42ee4c6e2279ab4a695b79a8bd60c5ede849b3

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding, Origin
content-encoding
gzip
etag
W/"3771d17eb46e31cbd97c55a477a47e57"
x-amz-version-id
null
via
1.1 2b13b2ad91208ea27acb039cde3e8f42.cloudfront.net (CloudFront)
x-cache
RefreshHit from cloudfront
x-amz-cf-id
MB4dfZ_H0dv9Oe_bVH3zhSnXbnoHJoDwWTCwI7D1KvaoIEvWiBpNYQ==
date
Thu, 01 Oct 2026 18:57:07 GMT
content-type
text/javascript
last-modified
Mon, 28 Sep 2026 12:38:55 GMT
server
AmazonS3
x-amz-cf-pop
AMS58-P3
x-amz-server-side-encryption
AES256
GET
H2
200
radio-api-live-broadcast
los40.com.pa/pf/api/v3/content/fetch/
4 KB
1 KB
869ms
868ms
Fetch
application/json
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/api/v3/content/fetch/radio-api-live-broadcast?query=%7B%22radioStationId%22%3A%22025000%22%2C%22date%22%3A%222026-10-01T20%253A57%253A00%252B02%253A00%22%2C%22itemsPerPage%22%3A3%2C%22imageCutCode%22%3A%22Rec_720x720%22%2C%22emissionType%22%3A%22Normal%22%7D&d=1025
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/pf/resources/js/libs/persistent-player.min.js?d=1025&mxId=00000000
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
Accept
application/json
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-security-policy
upgrade-insecure-requests
cache-control
max-age=3600
content-encoding
gzip
x-arc-ttl
3600
etag
W/"105e-B1yGRV+i5osUYOz1kQInf+e5tSA"
x-arc-pb-request-id
346ce16a-28cc-4591-9abb-25c8686bd02f
expires
Thu, 01 Oct 2026 19:57:06 GMT
content-length
833
date
Thu, 01 Oct 2026 18:57:06 GMT
x-arc-request-id
0.b2163017.1790881026.64a5
content-type
application/json; charset=utf-8
vary
Accept-Encoding
server
openresty
last-modified
Thu, 01 Oct 2026 18:57:06 GMT
GET
H2
200
style.css
player.prisamedia.com/core//skins/perm_musicales/css/
45 B
153 B
22ms
21ms
Stylesheet
text/css
199.232.198.133
Fastly
General
Full URL
https://player.prisamedia.com/core//skins/perm_musicales/css/style.css
Requested by
Host: player.prisamedia.com
URL: https://player.prisamedia.com/core//js/coreplayer.min.js
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
199.232.198.133 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
/
Resource Hash
386f61f76f2fd4164c973cfe038be172b139aea6b8d36d1c10ad9177a3f94052

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
"9fcee76d2c6484dcaa3722067a7a9210"
age
22095
x-timer
S1790881026.160365,VS0,VE0
via
1.1 varnish
accept-ranges
bytes
access-control-allow-origin
*
x-cache
HIT
content-length
63
date
Thu, 01 Oct 2026 18:57:06 GMT
last-modified
Thu, 01 Oct 2026 12:36:34 GMT
content-type
text/css; charset=utf-8
x-served-by
cache-lin1730051-LIN
x-cache-hits
31
vary
Accept-Encoding
GET
H2
200
template.html Show response
player.prisamedia.com/core//skins/perm_musicales/template/
2 KB
965 B
64ms
22ms
Fetch
text/html
199.232.198.133
Fastly
General
Full URL
https://player.prisamedia.com/core//skins/perm_musicales/template/template.html
Requested by
Host: player.prisamedia.com
URL: https://player.prisamedia.com/core//js/coreplayer.min.js
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
199.232.198.133 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
/
Resource Hash
5834080f39b7a4b2110cde1b11997cc54163b79b350de478daffb713717e9b32

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
etag
"c1e474468d4416a0676c00356ce455ac"
age
858
x-timer
S1790881026.224948,VS0,VE1
via
1.1 varnish
accept-ranges
bytes
access-control-allow-origin
*
x-cache
HIT
content-length
724
date
Thu, 01 Oct 2026 18:57:06 GMT
last-modified
Thu, 01 Oct 2026 12:36:34 GMT
content-type
text/html; charset=utf-8
x-served-by
cache-lin1730071-LIN
x-cache-hits
0
vary
Accept-Encoding
GET
H2
200
generic
match.adsrvr.org/track/cmf/ Frame 0222
70 B
149 B
135ms
42ms
Image
image/gif
35.71.131.137
Amazon.com
General
Full URL
https://match.adsrvr.org/track/cmf/generic?ttd_pid=aam&gdpr=0&gdpr_consent=&domain=los40.com.pa&ttd_tpi=1
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
35.71.131.137 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
a6370ebea231e0c9a.awsglobalaccelerator.com
Software
Kestrel /
Resource Hash
8d70b3e6badb6973663b398d297bb32eaedd08826a1af98d0a1cfce5324ffce0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://prisacom.demdex.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-length
70
date
Thu, 01 Oct 2026 18:57:06 GMT
content-type
image/gif
server
Kestrel
GET
H2
200
www-widgetapi.js Show response
www.youtube.com/s/player/8ab5c328/www-widgetapi.vflset/
26 KB
9 KB
18ms
17ms
Script
text/javascript
2001:4860:482b:400::
Google LLC
General
Full URL
https://www.youtube.com/s/player/8ab5c328/www-widgetapi.vflset/www-widgetapi.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/iframe_api
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:482b:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
c2dcf46501a48a87a7859596834012e81569a181f7b80bda4d91b04798f84751
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
127711
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Thu, 30 Sep 2027 07:28:35 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 30 Sep 2026 07:28:35 GMT
last-modified
Wed, 30 Sep 2026 04:27:49 GMT
content-type
text/javascript
vary
Accept-Encoding, Origin
cache-control
public, max-age=31536000
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
8877
x-xss-protection
0
server
sffe
POST
H2
200
interact Show response
edge.adobedc.net/ee/irl1/v1/
594 B
779 B
150ms
72ms
Fetch
application/json
63.140.62.139
Amazon.com
General
Full URL
https://edge.adobedc.net/ee/irl1/v1/interact?configId=9ad480a3-985a-4cc5-9907-d80eae43012e&requestId=e689e2db-ca0c-45ae-adcf-fa83d3218ec4
Requested by
Host: assets.adobedtm.com
URL: https://assets.adobedtm.com/0681c221600c/6fc9b54f3c25/launch-4756de8c2616.min.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
63.140.62.139 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ip-63-140-62-139.data.adobedc.net
Software
jag /
Resource Hash
dcc3f3a7421178e332078eebd53f187ba58159e706b3ddb19613d0ce89d882f0
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
Content-Type
text/plain; charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
x-request-id
e689e2db-ca0c-45ae-adcf-fa83d3218ec4-b46f8a4bee6f4edd
access-control-expose-headers
Retry-After, X-Adobe-Edge, X-Request-ID
cache-control
no-cache, no-store, max-age=0, no-transform, private
content-encoding
gzip
x-adobe-edge
IRL1;6
access-control-allow-credentials
true
x-content-type-options
nosniff
access-control-allow-origin
https://los40.com.pa
date
Thu, 01 Oct 2026 18:57:06 GMT
x-xss-protection
1; mode=block
x-konductor
26.9.5-HEAD-SNAPSHOT:f5db96293
vary
Origin
server
jag
content-type
application/json;charset=utf-8
GET
H3
200
fRIhCiUVaKs Show response
www.youtube.com/embed/ Frame 8D10
151 KB
60 KB
103ms
102ms
Document
text/html
142.251.155.119
Google LLC
General
Full URL
https://www.youtube.com/embed/fRIhCiUVaKs?enablejsapi=1
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.155.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
2d15b52e43fa02423bc0b9ba6f7987de39c81c4f53392554bd3332af5c60dab3
Security Headers
Name Value
Content-Security-Policy script-src 'unsafe-eval' 'self' 'unsafe-inline' https://www.google.com https://apis.google.com https://ssl.gstatic.com https://www.gstatic.com https://www.googletagmanager.com https://www.google-analytics.com https://*.youtube.com https://*.google.com https://*.gstatic.com https://youtube.com https://www.youtube.com https://google.com https://*.doubleclick.net https://*.googleapis.com https://www.googleadservices.com https://tpc.googlesyndication.com https://www.youtubekids.com https://www.youtube-nocookie.com https://www.youtubeeducation.com https://www-onepick-opensocial.googleusercontent.com;report-uri https://csp.withgoogle.com/csp/youtube_main/allowlist base-uri 'self';object-src 'none';script-src 'report-sample' 'nonce-g_ZdS05n3_WGsOfFsq81Cg' 'unsafe-inline' 'strict-dynamic' https: http: 'unsafe-eval';report-uri https://csp.withgoogle.com/csp/youtube_main/strict require-trusted-types-for 'script'
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://los40.com.pa/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cache-control
no-cache, no-store, max-age=0, must-revalidate
content-encoding
br
content-security-policy
script-src 'unsafe-eval' 'self' 'unsafe-inline' https://www.google.com https://apis.google.com https://ssl.gstatic.com https://www.gstatic.com https://www.googletagmanager.com https://www.google-analytics.com https://*.youtube.com https://*.google.com https://*.gstatic.com https://youtube.com https://www.youtube.com https://google.com https://*.doubleclick.net https://*.googleapis.com https://www.googleadservices.com https://tpc.googlesyndication.com https://www.youtubekids.com https://www.youtube-nocookie.com https://www.youtubeeducation.com https://www-onepick-opensocial.googleusercontent.com;report-uri https://csp.withgoogle.com/csp/youtube_main/allowlist base-uri 'self';object-src 'none';script-src 'report-sample' 'nonce-g_ZdS05n3_WGsOfFsq81Cg' 'unsafe-inline' 'strict-dynamic' https: http: 'unsafe-eval';report-uri https://csp.withgoogle.com/csp/youtube_main/strict require-trusted-types-for 'script'
content-type
text/html; charset=utf-8
cross-origin-embedder-policy-report-only
require-corp; report-to="youtube_main"
cross-origin-opener-policy-report-only
same-origin; report-to="youtube_main"
cross-origin-resource-policy
cross-origin
date
Thu, 01 Oct 2026 18:57:06 GMT
expires
Mon, 01 Jan 1990 00:00:00 GMT
origin-trial
AmhMBR6zCLzDDxpW+HfpP67BqwIknWnyMOXOQGfzYswFmJe+fgaI6XZgAzcxOrzNtP7hEDsOo1jdjFnVr2IdxQ4AAAB4eyJvcmlnaW4iOiJodHRwczovL3lvdXR1YmUuY29tOjQ0MyIsImZlYXR1cmUiOiJXZWJWaWV3WFJlcXVlc3RlZFdpdGhEZXByZWNhdGlvbiIsImV4cGlyeSI6MTc1ODA2NzE5OSwiaXNTdWJkb21haW4iOnRydWV9 AiDEBptUfVeO93q48VdVMe/ubupazdAl8AaHP+NBzdnW8quUcHdzJUyGSfrmtpKJu7EOvwRp9ug2rEo3XU+WMAMAAAB2eyJvcmlnaW4iOiJodHRwczovL3lvdXR1YmUuY29tOjQ0MyIsImZlYXR1cmUiOiJEZXZpY2VCb3VuZFNlc3Npb25DcmVkZW50aWFsczIiLCJleHBpcnkiOjE3NzQzMTA0MDAsImlzU3ViZG9tYWluIjp0cnVlfQ==
p3p
CP="This is not a P3P policy! See http://support.google.com/accounts/answer/151657?hl=de for more info."
permissions-policy
ch-ua-arch=*, ch-ua-bitness=*, ch-ua-full-version=*, ch-ua-full-version-list=*, ch-ua-model=*, ch-ua-wow64=*, ch-ua-form-factors=*, ch-ua-platform=*, ch-ua-platform-version=*
pragma
no-cache
report-to
{"group":"youtube_main","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube_main"}]}
server
ESF
strict-transport-security
max-age=31536000
vary
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
x-content-type-options
nosniff
x-xss-protection
0
POST
H3
200
log_event Show response
www.youtube.com/youtubei/v1/ Frame 8D10
28 B
50 B
40ms
37ms
XHR
application/json
142.251.155.119
Google LLC
General
Full URL
https://www.youtube.com/youtubei/v1/log_event?alt=json
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQADG/d=1/excm=base,root/br=1/rs=AGKMywHPwBmNjDXkqTzY4KDK4LnhoANgJg/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.155.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
scaffolding on HTTPServer2 /
Resource Hash
d7d5e54ad1e33d7ab49c664323ced79cb9723ff15e9764cd0edc3e15208e8336
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0
X-YouTube-Client-Name
56
X-YouTube-Ad-Signals
dt=1790881025334&flash=0&frm=2&u_tz=120&u_his=2&u_h=1200&u_w=1600&u_ah=1200&u_aw=1600&u_cd=24&bc=31&bih=-12245933&biw=-12245933&brdim=1570%2C1170%2C1570%2C1170%2C1600%2C0%2C1600%2C1200%2C453%2C255&vis=1&wgl=true&ca_type=image
X-Goog-Event-Time
1790881026227
X-YouTube-Client-Version
2.20261001.01.00
Content-Type
application/json
X-YouTube-Page-Label
youtube.embeds.web_20261001_01_RC00
X-YouTube-Page-CL
991486115
X-YouTube-Utc-Offset
120
Referer
https://www.youtube.com/embed/fRIhCiUVaKs
X-YouTube-Device
cbr=Chrome&cbrver=154.0.0.0&ceng=WebKit&cengver=537.36&cos=X11&cplatform=DESKTOP
X-Goog-Visitor-Id
CgtTN0pjUGtQVW5fZyiB2vrVBjIKCgJDSBIEGgAgT2LfAgrcAjIyLllUPUdGbmJDM2FwOFFTa3MzSXhkcDBVT04yTkdhMEJpazNKSDQ1OGJvYmFDRTgwS1R3QTh5T1Rhb2tuZjJvSlUtZ1ZTN0tOLUR0bDdYdkJiWE1QbEpqUnFPdWtzb2JZcG9CM1lwTjBJYlZQQU1ycFpuOEd1aEpMT2QydXlvZWI5QW90cGQtR1JlcUlYUDloVHM1enZaVENDWXdsOFV6Q3QtT19Vbm45NEExLUZ6MGJUMGI0ZjdsWFBsVTdJeWF1ZS1jWmJyMVNWRnExNGQ0a1E0a2xQSzFkQXM1dndaU0x0TG90aFBwd1hUT2drcTlldEV1dTJBWlZTeVVoX0hiU2hMd0xtR0kzZEpOSVJNbWUzOEJidjFiMkV1bXEwdkpiUVZpSVhkYXJLNW96dU5xd1Uxd3M1cW9TX2tjSlB0NW1LYS1wOHFqdmxWdlBaUVQxSm4ydzdEUzFJUQ%3D%3D
X-Goog-Request-Time
1790881026227
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
X-YouTube-Time-Zone
Europe/Zurich

Response headers

content-encoding
br
x-content-type-options
nosniff
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
31
date
Thu, 01 Oct 2026 18:57:06 GMT
x-xss-protection
0
content-type
application/json; charset=UTF-8
vary
Origin, X-Origin, Referer
server
scaffolding on HTTPServer2
x-frame-options
SAMEORIGIN
GET
H3
200
s3a4OQR-10M Show response
www.youtube.com/embed/ Frame CCE2
151 KB
60 KB
96ms
96ms
Document
text/html
142.251.155.119
Google LLC
General
Full URL
https://www.youtube.com/embed/s3a4OQR-10M?enablejsapi=1
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.155.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
43c743fa5a31cb96055d7933b5ef59a7cdcf22724de1ebdc162304ef3289b9e9
Security Headers
Name Value
Content-Security-Policy script-src 'unsafe-eval' 'self' 'unsafe-inline' https://www.google.com https://apis.google.com https://ssl.gstatic.com https://www.gstatic.com https://www.googletagmanager.com https://www.google-analytics.com https://*.youtube.com https://*.google.com https://*.gstatic.com https://youtube.com https://www.youtube.com https://google.com https://*.doubleclick.net https://*.googleapis.com https://www.googleadservices.com https://tpc.googlesyndication.com https://www.youtubekids.com https://www.youtube-nocookie.com https://www.youtubeeducation.com https://www-onepick-opensocial.googleusercontent.com;report-uri https://csp.withgoogle.com/csp/youtube_main/allowlist require-trusted-types-for 'script' base-uri 'self';object-src 'none';script-src 'report-sample' 'nonce-grgSB3eM2Xzj_AiSkXfwVg' 'unsafe-inline' 'strict-dynamic' https: http: 'unsafe-eval';report-uri https://csp.withgoogle.com/csp/youtube_main/strict
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://los40.com.pa/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cache-control
no-cache, no-store, max-age=0, must-revalidate
content-encoding
br
content-security-policy
script-src 'unsafe-eval' 'self' 'unsafe-inline' https://www.google.com https://apis.google.com https://ssl.gstatic.com https://www.gstatic.com https://www.googletagmanager.com https://www.google-analytics.com https://*.youtube.com https://*.google.com https://*.gstatic.com https://youtube.com https://www.youtube.com https://google.com https://*.doubleclick.net https://*.googleapis.com https://www.googleadservices.com https://tpc.googlesyndication.com https://www.youtubekids.com https://www.youtube-nocookie.com https://www.youtubeeducation.com https://www-onepick-opensocial.googleusercontent.com;report-uri https://csp.withgoogle.com/csp/youtube_main/allowlist require-trusted-types-for 'script' base-uri 'self';object-src 'none';script-src 'report-sample' 'nonce-grgSB3eM2Xzj_AiSkXfwVg' 'unsafe-inline' 'strict-dynamic' https: http: 'unsafe-eval';report-uri https://csp.withgoogle.com/csp/youtube_main/strict
content-type
text/html; charset=utf-8
cross-origin-embedder-policy-report-only
require-corp; report-to="youtube_main"
cross-origin-opener-policy-report-only
same-origin; report-to="youtube_main"
cross-origin-resource-policy
cross-origin
date
Thu, 01 Oct 2026 18:57:06 GMT
expires
Mon, 01 Jan 1990 00:00:00 GMT
origin-trial
AmhMBR6zCLzDDxpW+HfpP67BqwIknWnyMOXOQGfzYswFmJe+fgaI6XZgAzcxOrzNtP7hEDsOo1jdjFnVr2IdxQ4AAAB4eyJvcmlnaW4iOiJodHRwczovL3lvdXR1YmUuY29tOjQ0MyIsImZlYXR1cmUiOiJXZWJWaWV3WFJlcXVlc3RlZFdpdGhEZXByZWNhdGlvbiIsImV4cGlyeSI6MTc1ODA2NzE5OSwiaXNTdWJkb21haW4iOnRydWV9 AiDEBptUfVeO93q48VdVMe/ubupazdAl8AaHP+NBzdnW8quUcHdzJUyGSfrmtpKJu7EOvwRp9ug2rEo3XU+WMAMAAAB2eyJvcmlnaW4iOiJodHRwczovL3lvdXR1YmUuY29tOjQ0MyIsImZlYXR1cmUiOiJEZXZpY2VCb3VuZFNlc3Npb25DcmVkZW50aWFsczIiLCJleHBpcnkiOjE3NzQzMTA0MDAsImlzU3ViZG9tYWluIjp0cnVlfQ==
p3p
CP="This is not a P3P policy! See http://support.google.com/accounts/answer/151657?hl=de for more info."
permissions-policy
ch-ua-arch=*, ch-ua-bitness=*, ch-ua-full-version=*, ch-ua-full-version-list=*, ch-ua-model=*, ch-ua-wow64=*, ch-ua-form-factors=*, ch-ua-platform=*, ch-ua-platform-version=*
pragma
no-cache
report-to
{"group":"youtube_main","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube_main"}]}
server
ESF
strict-transport-security
max-age=31536000
vary
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
x-content-type-options
nosniff
x-xss-protection
0
POST
H3
200
log_event Show response
www.youtube.com/youtubei/v1/ Frame CCE2
28 B
50 B
45ms
41ms
XHR
application/json
142.251.155.119
Google LLC
General
Full URL
https://www.youtube.com/youtubei/v1/log_event?alt=json
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.155.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
scaffolding on HTTPServer2 /
Resource Hash
d7d5e54ad1e33d7ab49c664323ced79cb9723ff15e9764cd0edc3e15208e8336
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0
X-YouTube-Client-Name
56
X-YouTube-Ad-Signals
dt=1790881025362&flash=0&frm=2&u_tz=120&u_his=2&u_h=1200&u_w=1600&u_ah=1200&u_aw=1600&u_cd=24&bc=31&bih=-12245933&biw=-12245933&brdim=1570%2C1170%2C1570%2C1170%2C1600%2C0%2C1600%2C1200%2C0%2C0&vis=1&wgl=true&ca_type=image
X-Goog-Event-Time
1790881026231
X-YouTube-Client-Version
2.20261001.01.00
Content-Type
application/json
X-YouTube-Page-Label
youtube.embeds.web_20261001_01_RC00
X-YouTube-Page-CL
991486115
X-YouTube-Utc-Offset
120
Referer
https://www.youtube.com/embed/s3a4OQR-10M
X-YouTube-Device
cbr=Chrome&cbrver=154.0.0.0&ceng=WebKit&cengver=537.36&cos=X11&cplatform=DESKTOP
X-Goog-Visitor-Id
CgsweHpDLUo2ZTUxUSiB2vrVBjIKCgJDSBIEGgAgPmLfAgrcAjIyLllUPUlkQUN4ejFSU25VNUVpYkVQdkxSY0kxTHhfaXJUMHdselQ3YWdTcnNoeFFoOFdnYkVfOUp4RnZKb0Z5SlprOXZkU1ZmakhteS1SWk5WQU9DbFNpT01zOVYzLXNjRnRsaEo2SGNFelJNb2tKZDQ2a1VpZ3pWWU1hQURoX2EzZnVjdmozNWpwVzBab2RPRkNSWl84LXhkS2QtTHJib0lQRGdGMWpPNENHOWFLMzMxNE1POV83QUw1SFVKRDJUNnp3SWgwMEZnRWhYYXUzOGtJVjhWTm02c213aTJMRktaTjYtRlFGYkl6TUhKZDhIY01fQUM0V191UGZEWklkNW1DSUN6aW1CX2F1ZDBPS1F3cVhzTzE4ODRpZXNqM2xscGI0VmRqTk1Sak05UWszQnRwdF91eWpmbXJRYmlwWUVlZmd0MjlkR3NpVEZvd0ZBbVMydjZ6c201dw%3D%3D
X-Goog-Request-Time
1790881026232
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
X-YouTube-Time-Zone
Europe/Zurich

Response headers

content-encoding
br
x-content-type-options
nosniff
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
31
date
Thu, 01 Oct 2026 18:57:06 GMT
x-xss-protection
0
content-type
application/json; charset=UTF-8
vary
Origin, X-Origin, Referer
server
scaffolding on HTTPServer2
x-frame-options
SAMEORIGIN
GET
H3
200
_1W51TfwOEA Show response
www.youtube.com/embed/ Frame B420
152 KB
60 KB
112ms
112ms
Document
text/html
142.251.155.119
Google LLC
General
Full URL
https://www.youtube.com/embed/_1W51TfwOEA?enablejsapi=1
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.155.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
84da29e74152c5f3bb82157c74c24304090541c602ded4207d9e9e18b7283dbd
Security Headers
Name Value
Content-Security-Policy script-src 'unsafe-eval' 'self' 'unsafe-inline' https://www.google.com https://apis.google.com https://ssl.gstatic.com https://www.gstatic.com https://www.googletagmanager.com https://www.google-analytics.com https://*.youtube.com https://*.google.com https://*.gstatic.com https://youtube.com https://www.youtube.com https://google.com https://*.doubleclick.net https://*.googleapis.com https://www.googleadservices.com https://tpc.googlesyndication.com https://www.youtubekids.com https://www.youtube-nocookie.com https://www.youtubeeducation.com https://www-onepick-opensocial.googleusercontent.com;report-uri https://csp.withgoogle.com/csp/youtube_main/allowlist require-trusted-types-for 'script' base-uri 'self';object-src 'none';script-src 'report-sample' 'nonce-McEEyWgzTwrYiC2DPW15TA' 'unsafe-inline' 'strict-dynamic' https: http: 'unsafe-eval';report-uri https://csp.withgoogle.com/csp/youtube_main/strict
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://los40.com.pa/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

accept-ch
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cache-control
no-cache, no-store, max-age=0, must-revalidate
content-encoding
br
content-security-policy
script-src 'unsafe-eval' 'self' 'unsafe-inline' https://www.google.com https://apis.google.com https://ssl.gstatic.com https://www.gstatic.com https://www.googletagmanager.com https://www.google-analytics.com https://*.youtube.com https://*.google.com https://*.gstatic.com https://youtube.com https://www.youtube.com https://google.com https://*.doubleclick.net https://*.googleapis.com https://www.googleadservices.com https://tpc.googlesyndication.com https://www.youtubekids.com https://www.youtube-nocookie.com https://www.youtubeeducation.com https://www-onepick-opensocial.googleusercontent.com;report-uri https://csp.withgoogle.com/csp/youtube_main/allowlist require-trusted-types-for 'script' base-uri 'self';object-src 'none';script-src 'report-sample' 'nonce-McEEyWgzTwrYiC2DPW15TA' 'unsafe-inline' 'strict-dynamic' https: http: 'unsafe-eval';report-uri https://csp.withgoogle.com/csp/youtube_main/strict
content-type
text/html; charset=utf-8
cross-origin-embedder-policy-report-only
require-corp; report-to="youtube_main"
cross-origin-opener-policy-report-only
same-origin; report-to="youtube_main"
cross-origin-resource-policy
cross-origin
date
Thu, 01 Oct 2026 18:57:06 GMT
expires
Mon, 01 Jan 1990 00:00:00 GMT
origin-trial
AmhMBR6zCLzDDxpW+HfpP67BqwIknWnyMOXOQGfzYswFmJe+fgaI6XZgAzcxOrzNtP7hEDsOo1jdjFnVr2IdxQ4AAAB4eyJvcmlnaW4iOiJodHRwczovL3lvdXR1YmUuY29tOjQ0MyIsImZlYXR1cmUiOiJXZWJWaWV3WFJlcXVlc3RlZFdpdGhEZXByZWNhdGlvbiIsImV4cGlyeSI6MTc1ODA2NzE5OSwiaXNTdWJkb21haW4iOnRydWV9 AiDEBptUfVeO93q48VdVMe/ubupazdAl8AaHP+NBzdnW8quUcHdzJUyGSfrmtpKJu7EOvwRp9ug2rEo3XU+WMAMAAAB2eyJvcmlnaW4iOiJodHRwczovL3lvdXR1YmUuY29tOjQ0MyIsImZlYXR1cmUiOiJEZXZpY2VCb3VuZFNlc3Npb25DcmVkZW50aWFsczIiLCJleHBpcnkiOjE3NzQzMTA0MDAsImlzU3ViZG9tYWluIjp0cnVlfQ==
p3p
CP="This is not a P3P policy! See http://support.google.com/accounts/answer/151657?hl=de for more info."
permissions-policy
ch-ua-arch=*, ch-ua-bitness=*, ch-ua-full-version=*, ch-ua-full-version-list=*, ch-ua-model=*, ch-ua-wow64=*, ch-ua-form-factors=*, ch-ua-platform=*, ch-ua-platform-version=*
pragma
no-cache
report-to
{"group":"youtube_main","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube_main"}]}
server
ESF
strict-transport-security
max-age=31536000
vary
Sec-CH-UA-Arch, Sec-CH-UA-Bitness, Sec-CH-UA-Full-Version, Sec-CH-UA-Full-Version-List, Sec-CH-UA-Model, Sec-CH-UA-WoW64, Sec-CH-UA-Form-Factors, Sec-CH-UA-Platform, Sec-CH-UA-Platform-Version
x-content-type-options
nosniff
x-xss-protection
0
POST
H3
200
log_event Show response
www.youtube.com/youtubei/v1/ Frame B420
28 B
50 B
51ms
47ms
XHR
application/json
142.251.155.119
Google LLC
General
Full URL
https://www.youtube.com/youtubei/v1/log_event?alt=json
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.155.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
scaffolding on HTTPServer2 /
Resource Hash
d7d5e54ad1e33d7ab49c664323ced79cb9723ff15e9764cd0edc3e15208e8336
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0
X-YouTube-Client-Name
56
X-YouTube-Ad-Signals
dt=1790881025354&flash=0&frm=2&u_tz=120&u_his=2&u_h=1200&u_w=1600&u_ah=1200&u_aw=1600&u_cd=24&bc=31&bih=-12245933&biw=-12245933&brdim=1570%2C1170%2C1570%2C1170%2C1600%2C0%2C1600%2C1200%2C0%2C0&vis=1&wgl=true&ca_type=image
X-Goog-Event-Time
1790881026235
X-YouTube-Client-Version
2.20261001.01.00
Content-Type
application/json
X-YouTube-Page-Label
youtube.embeds.web_20261001_01_RC00
X-YouTube-Page-CL
991486115
X-YouTube-Utc-Offset
120
Referer
https://www.youtube.com/embed/_1W51TfwOEA
X-YouTube-Device
cbr=Chrome&cbrver=154.0.0.0&ceng=WebKit&cengver=537.36&cos=X11&cplatform=DESKTOP
X-Goog-Visitor-Id
CgsxT1FKWXBldDhjbyiB2vrVBjIKCgJDSBIEGgAgJ2LfAgrcAjIyLllUPVVYVHRXdXByd2tGSl8tNzRhQmRoRU5GWEJELTE3T2xDNkJKOGpUMEs1NXlZMkk5UzlHZ2k0WE16Nm1ORmk2aVEzUl91d2ZwdmZ3LVozcEpkUGFNTjJEdERvM2YwaURwUEhITUE0YWVneUZhRm84NHY3c3dVX2pSbDNxVG5XaktaMHdDekNCSGhuN18tX3JzYmlXVmgxWE1FT2ktbExBR1d4WWE1YU01aFRZRTBRd1JyMTlPV2hueERsNW5xbk52U2NVODhUSnFtTmtzUU1kbVllMUxJZ2czaHVGcmpjR2FpWE1taGg2Vi1NY1RNUWQteUJrYWpieDRLTlVGeTA4N2tPVUdTeC1rZ09UaFRxbzRZdnNtNlhNTVBNdk1uSXNXS2hibkt6QThFYU1JcmUwLVd0WFFnNnJmYnRhTHhaQnpQYXZDa21YckcwSTQwRkU1V2xuQnREUQ%3D%3D
X-Goog-Request-Time
1790881026235
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
X-YouTube-Time-Zone
Europe/Zurich

Response headers

content-encoding
br
x-content-type-options
nosniff
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
31
date
Thu, 01 Oct 2026 18:57:06 GMT
x-xss-protection
0
content-type
application/json; charset=UTF-8
vary
Origin, X-Origin, Referer
server
scaffolding on HTTPServer2
x-frame-options
SAMEORIGIN
GET
H2
200
3226 Show response
config.aps.amazon-adsystem.com/configs/
2 KB
1 KB
102ms
30ms
Script
application/javascript
18.238.243.129
Amazon.com
General
Full URL
https://config.aps.amazon-adsystem.com/configs/3226
Requested by
Host: c.amazon-adsystem.com
URL: https://c.amazon-adsystem.com/aax2/apstag.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
18.238.243.129 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-18-238-243-129.ams58.r.cloudfront.net
Software
/
Resource Hash
746545703d9d979d390b0e042dcec5134b82c94247e69c5f6dbf50094d38e015

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=3600
content-encoding
gzip
age
1454
via
1.1 432282689bafd802e8ec9636c256a3b0.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
content-length
840
x-amz-cf-id
sy8pSO4qNfteanadlslZl0OtoAylbZCoRKzBb5jvId1wSPPgX1q6xQ==
date
Thu, 01 Oct 2026 18:32:51 GMT
content-type
application/javascript
x-amz-cf-pop
AMS58-P1
GET
H2
200
aps_csm.js Show response
c.amazon-adsystem.com/bao-csm/aps-comm/
6 KB
3 KB
97ms
40ms
XHR
application/javascript
3.173.128.89
Amazon.com
General
Full URL
https://c.amazon-adsystem.com/bao-csm/aps-comm/aps_csm.js
Requested by
Host: c.amazon-adsystem.com
URL: https://c.amazon-adsystem.com/aax2/apstag.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.173.128.89 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-173-128-89.ams56.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
06b99248a163333e36980a6cfb756f1a7de60fa49517162b87b1a44d5d48f844

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

access-control-max-age
3000
content-encoding
gzip
x-amz-version-id
r5.lR.LJ66XEXzxUUVo7iMemjL_F_GoE
etag
W/"a4d296427fc806b21335359e398c025c"
age
40151
access-control-allow-methods
GET
x-cache
Hit from cloudfront
x-amz-cf-id
JVkYX2aHwRKGHJLLkKWqpOBfNuvvk0bwnaJR2GMKPqu8Psz7MSdpEQ==
date
Thu, 01 Oct 2026 07:47:56 GMT
content-type
application/javascript
vary
Origin,Accept-Encoding
last-modified
Thu, 29 Feb 2024 02:13:08 GMT
cache-control
public, max-age=86400
via
1.1 b692bc875a355cf4bcfdf091c20312fc.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-amz-cf-pop
AMS56-P1
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H2
200
ibs:dpid=19566&dpuuid=2D34D10C-38AF-4AA3-ACA5-B11BDA5E79D1
dpm.demdex.net/ Frame 0222
Redirect Chain
  • https://image6.pubmatic.com/AdServer/UCookieSetPug?p=166334&rd=https%3A%2F%2Fdpm.demdex.net%2Fibs%3Adpid=19566%26dpuuid=%23PM_USER_ID
  • https://image6.pubmatic.com/AdServer/UCookieSetPug?p=166334&rd=https%3A%2F%2Fdpm.demdex.net%2Fibs%3Adpid=19566%26dpuuid=%23PM_USER_ID&rdf=1
  • https://dpm.demdex.net/ibs:dpid=19566&dpuuid=2D34D10C-38AF-4AA3-ACA5-B11BDA5E79D1
42 B
703 B
55ms
52ms
Image
image/gif
52.17.233.147
Amazon.com
General
Full URL
https://dpm.demdex.net/ibs:dpid=19566&dpuuid=2D34D10C-38AF-4AA3-ACA5-B11BDA5E79D1
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Server
52.17.233.147 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-52-17-233-147.eu-west-1.compute.amazonaws.com
Software
/
Resource Hash
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Content-Type-Options nosniff

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
Referer
https://prisacom.demdex.net/

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
no-cache,no-store,must-revalidate,max-age=0,proxy-revalidate,no-transform,private
dcs
dcs-prod-irl1-1-v097-03e526aff.edge-irl1.demdex.com 7 ms
content-encoding
zstd
pragma
no-cache
x-content-type-options
nosniff
x-tid
yIMkFd0p/nA=
expires
Thu, 01 Jan 1970 00:00:00 UTC
content-length
46
p3p
policyref="/w3c/p3p.xml", CP="NOI NID CURa ADMa DEVa PSAa PSDa OUR SAMa BUS PUR COM NAV INT"
date
Thu, 01 Oct 2026 18:57:06 GMT
content-type
image/gif

Redirect headers

strict-transport-security
max-age=16070400; includeSubDomains
location
https://dpm.demdex.net/ibs:dpid=19566&dpuuid=2D34D10C-38AF-4AA3-ACA5-B11BDA5E79D1
p3p
CP="NOI DSP COR LAW CUR ADMo DEVo TAIo PSAo PSDo IVAo IVDo HISo OTPo OUR SAMo BUS UNI COM NAV INT DEM CNT STA PRE LOC"
content-length
0
date
Thu, 01 Oct 2026 18:57:06 GMT
content-type
text/html; charset=UTF-8
POST

atr
www.youtube.com/api/stats/ Frame CCE2
0
0


POST

log_event
www.youtube.com/youtubei/v1/ Frame CCE2
0
0


GET
H2
200
www-player.css
www.youtube.com/s/player/8ab5c328/ Frame CCE2
532 KB
0
1ms
1ms
Stylesheet
text/css
2001:4860:4826:400::
Google LLC
General
Full URL
https://www.youtube.com/s/player/8ab5c328/www-player.css
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/s3a4OQR-10M?enablejsapi=1
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:4826:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
3c9902065d76c2e9cf04e2d7555f6a3e2ff55f17f2956e3389dbdc836ff15d31
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/s3a4OQR-10M?enablejsapi=1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
34336
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 09:24:49 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 09:24:49 GMT
last-modified
Wed, 30 Sep 2026 04:27:49 GMT
content-type
text/css
vary
Accept-Encoding, Origin
cache-control
public, max-age=31536000
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
58415
x-xss-protection
0
server
sffe
GET
H2
200
m=root,base
www.youtube.com/s/_/ytembeds/_/ss/k=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/br=1/rs=AGKMywG-lxu8F22vbSId3KyWJKWKvkEUvg/ Frame CCE2
0
0
3ms
3ms
Stylesheet
text/css
2001:4860:4826:400::
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/ss/k=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/br=1/rs=AGKMywG-lxu8F22vbSId3KyWJKWKvkEUvg/m=root,base
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/s3a4OQR-10M?enablejsapi=1
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:4826:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/s3a4OQR-10M?enablejsapi=1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

age
22119
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 12:48:26 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 12:48:26 GMT
last-modified
Wed, 30 Sep 2026 19:08:25 GMT
content-type
text/css; charset=UTF-8
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
0
x-xss-protection
0
server
sffe
GET
H3
200
m=root,base Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/ Frame CCE2
458 KB
0
3ms
3ms
Script
text/javascript
142.251.154.4
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/s3a4OQR-10M?enablejsapi=1
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.154.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
43f040f22fdc551d207513b8e2b7be100273ff01f221dbdbb95e0d3cee9ba2b8
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/s3a4OQR-10M?enablejsapi=1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
22072
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 12:49:13 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 12:49:13 GMT
last-modified
Thu, 01 Oct 2026 03:06:41 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
159418
x-xss-protection
0
server
sffe
GET
H2
200
base.js Show response
www.youtube.com/s/player/8ab5c328/player_embed_es6.vflset/de_DE/ Frame CCE2
2 MB
0
3ms
3ms
Script
text/javascript
2001:4860:4826:400::
Google LLC
General
Full URL
https://www.youtube.com/s/player/8ab5c328/player_embed_es6.vflset/de_DE/base.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/s3a4OQR-10M?enablejsapi=1
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:4826:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
db6ad205995da14e082e8522a7a82ca52aa824efdb0cad8dadbabf5ffca2faf1
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/s3a4OQR-10M?enablejsapi=1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
127639
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Thu, 30 Sep 2027 07:29:46 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 30 Sep 2026 07:29:46 GMT
last-modified
Wed, 30 Sep 2026 04:27:49 GMT
content-type
text/javascript
vary
Accept-Encoding, Origin
cache-control
public, max-age=31536000
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
486502
x-xss-protection
0
server
sffe
POST

atr
www.youtube.com/api/stats/ Frame 8D10
0
0


POST

log_event
www.youtube.com/youtubei/v1/ Frame 8D10
0
0


GET
H2
200
www-player.css
www.youtube.com/s/player/8ab5c328/ Frame 8D10
532 KB
0
0ms
0ms
Stylesheet
text/css
2001:4860:4826:400::
Google LLC
General
Full URL
https://www.youtube.com/s/player/8ab5c328/www-player.css
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/fRIhCiUVaKs?enablejsapi=1
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:4826:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
3c9902065d76c2e9cf04e2d7555f6a3e2ff55f17f2956e3389dbdc836ff15d31
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/fRIhCiUVaKs?enablejsapi=1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
34336
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 09:24:49 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 09:24:49 GMT
last-modified
Wed, 30 Sep 2026 04:27:49 GMT
content-type
text/css
vary
Accept-Encoding, Origin
cache-control
public, max-age=31536000
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
58415
x-xss-protection
0
server
sffe
GET
H2
200
m=root,base
www.youtube.com/s/_/ytembeds/_/ss/k=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/br=1/rs=AGKMywG-lxu8F22vbSId3KyWJKWKvkEUvg/ Frame 8D10
0
0
3ms
3ms
Stylesheet
text/css
2001:4860:4826:400::
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/ss/k=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/br=1/rs=AGKMywG-lxu8F22vbSId3KyWJKWKvkEUvg/m=root,base
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/fRIhCiUVaKs?enablejsapi=1
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:4826:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/fRIhCiUVaKs?enablejsapi=1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

age
22119
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 12:48:26 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 12:48:26 GMT
last-modified
Wed, 30 Sep 2026 19:08:25 GMT
content-type
text/css; charset=UTF-8
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
0
x-xss-protection
0
server
sffe
GET
H3
200
m=root,base Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/ Frame 8D10
458 KB
0
3ms
3ms
Script
text/javascript
142.251.154.4
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/fRIhCiUVaKs?enablejsapi=1
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.154.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
43f040f22fdc551d207513b8e2b7be100273ff01f221dbdbb95e0d3cee9ba2b8
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/fRIhCiUVaKs?enablejsapi=1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
22072
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 12:49:13 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 12:49:13 GMT
last-modified
Thu, 01 Oct 2026 03:06:41 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
159418
x-xss-protection
0
server
sffe
GET
H2
200
base.js Show response
www.youtube.com/s/player/8ab5c328/player_embed_es6.vflset/de_DE/ Frame 8D10
2 MB
0
4ms
4ms
Script
text/javascript
2001:4860:4826:400::
Google LLC
General
Full URL
https://www.youtube.com/s/player/8ab5c328/player_embed_es6.vflset/de_DE/base.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/fRIhCiUVaKs?enablejsapi=1
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:4826:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
db6ad205995da14e082e8522a7a82ca52aa824efdb0cad8dadbabf5ffca2faf1
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/fRIhCiUVaKs?enablejsapi=1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
127639
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Thu, 30 Sep 2027 07:29:46 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 30 Sep 2026 07:29:46 GMT
last-modified
Wed, 30 Sep 2026 04:27:49 GMT
content-type
text/javascript
vary
Accept-Encoding, Origin
cache-control
public, max-age=31536000
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
486502
x-xss-protection
0
server
sffe
POST

atr
www.youtube.com/api/stats/ Frame B420
0
0


POST

log_event
www.youtube.com/youtubei/v1/ Frame B420
0
0


GET
H2
200
www-player.css
www.youtube.com/s/player/8ab5c328/ Frame B420
532 KB
0
0ms
0ms
Stylesheet
text/css
2001:4860:4826:400::
Google LLC
General
Full URL
https://www.youtube.com/s/player/8ab5c328/www-player.css
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/_1W51TfwOEA?enablejsapi=1
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:4826:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
3c9902065d76c2e9cf04e2d7555f6a3e2ff55f17f2956e3389dbdc836ff15d31
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/_1W51TfwOEA?enablejsapi=1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
34336
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 09:24:49 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 09:24:49 GMT
last-modified
Wed, 30 Sep 2026 04:27:49 GMT
content-type
text/css
vary
Accept-Encoding, Origin
cache-control
public, max-age=31536000
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
58415
x-xss-protection
0
server
sffe
GET
H2
200
m=root,base
www.youtube.com/s/_/ytembeds/_/ss/k=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/br=1/rs=AGKMywG-lxu8F22vbSId3KyWJKWKvkEUvg/ Frame B420
0
0
3ms
3ms
Stylesheet
text/css
2001:4860:4826:400::
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/ss/k=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/br=1/rs=AGKMywG-lxu8F22vbSId3KyWJKWKvkEUvg/m=root,base
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/_1W51TfwOEA?enablejsapi=1
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:4826:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/_1W51TfwOEA?enablejsapi=1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

age
22119
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 12:48:26 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 12:48:26 GMT
last-modified
Wed, 30 Sep 2026 19:08:25 GMT
content-type
text/css; charset=UTF-8
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
0
x-xss-protection
0
server
sffe
GET
H3
200
m=root,base Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/ Frame B420
458 KB
0
3ms
3ms
Script
text/javascript
142.251.154.4
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/_1W51TfwOEA?enablejsapi=1
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.154.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
43f040f22fdc551d207513b8e2b7be100273ff01f221dbdbb95e0d3cee9ba2b8
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/_1W51TfwOEA?enablejsapi=1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
22072
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 12:49:13 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 12:49:13 GMT
last-modified
Thu, 01 Oct 2026 03:06:41 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
159418
x-xss-protection
0
server
sffe
GET
H2
200
base.js Show response
www.youtube.com/s/player/8ab5c328/player_embed_es6.vflset/de_DE/ Frame B420
2 MB
0
3ms
3ms
Script
text/javascript
2001:4860:4826:400::
Google LLC
General
Full URL
https://www.youtube.com/s/player/8ab5c328/player_embed_es6.vflset/de_DE/base.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/_1W51TfwOEA?enablejsapi=1
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2001:4860:4826:400:: , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
db6ad205995da14e082e8522a7a82ca52aa824efdb0cad8dadbabf5ffca2faf1
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/_1W51TfwOEA?enablejsapi=1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
127639
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Thu, 30 Sep 2027 07:29:46 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 30 Sep 2026 07:29:46 GMT
last-modified
Wed, 30 Sep 2026 04:27:49 GMT
content-type
text/javascript
vary
Accept-Encoding, Origin
cache-control
public, max-age=31536000
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
486502
x-xss-protection
0
server
sffe
GET
H3
200
KFO7CnqEu92Fr1ME7kSn66aGLdTylUAMa3yUBA.woff2
fonts.gstatic.com/s/roboto/v48/ Frame CCE2
39 KB
0
2ms
2ms
Font
font/woff2
142.251.110.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/roboto/v48/KFO7CnqEu92Fr1ME7kSn66aGLdTylUAMa3yUBA.woff2
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/s3a4OQR-10M?enablejsapi=1
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.110.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f94.1e100.net
Software
sffe /
Resource Hash
20b535fa80c8189e3b87d1803038389960203a886d502bc2ef1857affc2f38d2
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://www.youtube.com
sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

age
31185
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 10:17:20 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 10:17:20 GMT
last-modified
Thu, 29 May 2025 23:30:55 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
40128
x-xss-protection
0
server
sffe
GET
H3
200
KFO7CnqEu92Fr1ME7kSn66aGLdTylUAMa3yUBA.woff2
fonts.gstatic.com/s/roboto/v48/ Frame 8D10
39 KB
0
2ms
2ms
Font
font/woff2
142.251.110.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/roboto/v48/KFO7CnqEu92Fr1ME7kSn66aGLdTylUAMa3yUBA.woff2
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/fRIhCiUVaKs?enablejsapi=1
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.110.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f94.1e100.net
Software
sffe /
Resource Hash
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://www.youtube.com
Referer
https://www.youtube.com/

Response headers

age
31185
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 10:17:20 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 10:17:20 GMT
last-modified
Thu, 29 May 2025 23:30:55 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
40128
x-xss-protection
0
server
sffe
GET
H3
200
KFO7CnqEu92Fr1ME7kSn66aGLdTylUAMa3yUBA.woff2
fonts.gstatic.com/s/roboto/v48/ Frame B420
39 KB
0
2ms
2ms
Font
font/woff2
142.251.110.94
Google LLC
General
Full URL
https://fonts.gstatic.com/s/roboto/v48/KFO7CnqEu92Fr1ME7kSn66aGLdTylUAMa3yUBA.woff2
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/_1W51TfwOEA?enablejsapi=1
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.110.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f94.1e100.net
Software
sffe /
Resource Hash
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Origin
https://www.youtube.com
Referer
https://www.youtube.com/

Response headers

age
31185
report-to
{"group":"apps-themes","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/apps-themes"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 10:17:20 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 10:17:20 GMT
last-modified
Thu, 29 May 2025 23:30:55 GMT
content-type
font/woff2
cache-control
public, max-age=31536000
timing-allow-origin
*
cross-origin-opener-policy
same-origin; report-to="apps-themes"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/apps-themes
accept-ranges
bytes
access-control-allow-origin
*
content-length
40128
x-xss-protection
0
server
sffe
GET
H2
200
ibs:dpid=175765&dpuuid=ea796336d9dc2cd9f6ef31d5042f4773
dpm.demdex.net/ Frame 0222
Redirect Chain
  • https://synchroscript.deliveryengine.adswizz.com/getUID?curl=https%3A%2F%2Fdpm.demdex.net%2Fibs%3Adpid%3D175765%26dpuuid%3D%24%7BUID%7D
  • https://dpm.demdex.net/ibs:dpid=175765&dpuuid=ea796336d9dc2cd9f6ef31d5042f4773
42 B
703 B
47ms
46ms
Image
image/gif
52.17.233.147
Amazon.com
General
Full URL
https://dpm.demdex.net/ibs:dpid=175765&dpuuid=ea796336d9dc2cd9f6ef31d5042f4773
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Server
52.17.233.147 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-52-17-233-147.eu-west-1.compute.amazonaws.com
Software
/
Resource Hash
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Content-Type-Options nosniff

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
Referer
https://prisacom.demdex.net/

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
no-cache,no-store,must-revalidate,max-age=0,proxy-revalidate,no-transform,private
dcs
dcs-prod-irl1-2-v097-01f709f00.edge-irl1.demdex.com 2 ms
content-encoding
zstd
pragma
no-cache
x-content-type-options
nosniff
x-tid
ESIO/0iP4B8=
expires
Thu, 01 Jan 1970 00:00:00 UTC
content-length
46
p3p
policyref="/w3c/p3p.xml", CP="NOI NID CURa ADMa DEVa PSAa PSDa OUR SAMa BUS PUR COM NAV INT"
date
Thu, 01 Oct 2026 18:57:06 GMT
content-type
image/gif

Redirect headers

x-adswizz-request-id
8251115c-ab07-4452-b159-b7b9b7ae607e
location
https://dpm.demdex.net/ibs:dpid=175765&dpuuid=ea796336d9dc2cd9f6ef31d5042f4773
x-clacks-overhead
GNU Terry Pratchett
via
1.1 ad3a844607df41a7152eab5ebe6e4056.cloudfront.net (CloudFront)
x-cache
Miss from cloudfront
x-amz-cf-id
TFJy9LoLvop5TNWb4gN98D7OSnyI-bYA1iXwdwrm1ZHl1fFqH3v1ow==
date
Thu, 01 Oct 2026 18:57:06 GMT
x-amz-cf-pop
FRA56-P9
GET
H3
200
id Show response
googleads.g.doubleclick.net/pagead/ Frame CCE2
113 B
159 B
62ms
62ms
XHR
application/json
142.251.110.154
Google LLC
General
Full URL
https://googleads.g.doubleclick.net/pagead/id
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.110.154 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f154.1e100.net
Software
cafe /
Resource Hash
0aa0f96f7bd97efa74470d5d766aebc7f1892c1b3a27326b02567754ee3fbb08
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
date
Thu, 01 Oct 2026 18:57:06 GMT
content-type
application/json; charset=UTF-8
content-disposition
attachment; filename="f.txt"
cache-control
no-cache, no-store, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
access-control-allow-origin
https://www.youtube.com
content-length
133
x-xss-protection
0
server
cafe
GET
H2
200
ad_status.js Show response
static.doubleclick.net/instream/ Frame CCE2
29 B
0
0ms
0ms
Script
text/javascript
2a00:1450:4001:c15::95
Google LLC
General
Full URL
https://static.doubleclick.net/instream/ad_status.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a00:1450:4001:c15::95 Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
eed0dc1fdb5d97ed188ae16fd5e1024a5bb744af47340346be2146300a6c54b9
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

age
782
report-to
{"group":"ads-doubleclick-media","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/ads-doubleclick-media"}]}
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 18:59:03 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 18:44:03 GMT
last-modified
Thu, 12 Dec 2013 23:40:16 GMT
content-type
text/javascript
cache-control
public, max-age=900
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to="ads-doubleclick-media"
content-length
29
x-xss-protection
0
server
sffe
GET
H3
200
m=r78Drb Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/ck=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/exm=base,root/excm=base,root/ed=1/br=1/rs=AGKMywESyf9Y9X87KVWSKj1IXnBDyFL... Frame CCE2
914 KB
0
0ms
0ms
Script
text/javascript
142.251.154.4
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/ck=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/exm=base,root/excm=base,root/ed=1/br=1/rs=AGKMywESyf9Y9X87KVWSKj1IXnBDyFLpDQ/m=r78Drb
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.154.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
ca01e9635150b32eea34bab004744a814e45a564585eeb9a572af2120e9091c4
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/s3a4OQR-10M?enablejsapi=1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
22072
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 12:49:13 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 12:49:13 GMT
last-modified
Wed, 30 Sep 2026 19:08:25 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
226102
x-xss-protection
0
server
sffe
GET
H3
200
id Show response
googleads.g.doubleclick.net/pagead/ Frame 8D10
113 B
159 B
105ms
62ms
XHR
application/json
142.251.110.154
Google LLC
General
Full URL
https://googleads.g.doubleclick.net/pagead/id
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.110.154 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f154.1e100.net
Software
cafe /
Resource Hash
1022bdddc3d32541a12cc7856a51b713e92ffd50ae0691f826a5418a366f54b5
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
date
Thu, 01 Oct 2026 18:57:06 GMT
content-type
application/json; charset=UTF-8
content-disposition
attachment; filename="f.txt"
cache-control
no-cache, no-store, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
access-control-allow-origin
https://www.youtube.com
content-length
133
x-xss-protection
0
server
cafe
GET
H2
200
ad_status.js Show response
static.doubleclick.net/instream/ Frame 8D10
29 B
0
0ms
0ms
Script
text/javascript
2a00:1450:4001:c15::95
Google LLC
General
Full URL
https://static.doubleclick.net/instream/ad_status.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a00:1450:4001:c15::95 Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
eed0dc1fdb5d97ed188ae16fd5e1024a5bb744af47340346be2146300a6c54b9
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

age
782
report-to
{"group":"ads-doubleclick-media","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/ads-doubleclick-media"}]}
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 18:59:03 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 18:44:03 GMT
last-modified
Thu, 12 Dec 2013 23:40:16 GMT
content-type
text/javascript
cache-control
public, max-age=900
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to="ads-doubleclick-media"
content-length
29
x-xss-protection
0
server
sffe
GET
H3
200
m=r78Drb Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/ck=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/exm=base,root/excm=base,root/ed=1/br=1/rs=AGKMywESyf9Y9X87KVWSKj1IXnBDyFL... Frame 8D10
914 KB
0
0ms
0ms
Script
text/javascript
142.251.154.4
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/ck=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/exm=base,root/excm=base,root/ed=1/br=1/rs=AGKMywESyf9Y9X87KVWSKj1IXnBDyFLpDQ/m=r78Drb
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.154.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
ca01e9635150b32eea34bab004744a814e45a564585eeb9a572af2120e9091c4
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/fRIhCiUVaKs?enablejsapi=1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
22072
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 12:49:13 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 12:49:13 GMT
last-modified
Wed, 30 Sep 2026 19:08:25 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
226102
x-xss-protection
0
server
sffe
GET
H3
200
4pMmjwvOS2kjRCXjDCV7i2J4CsXNLQ2vv-HF0yIf4DU.js Show response
www.google.com/js/th/ Frame CCE2
61 KB
24 KB
19ms
18ms
Script
text/javascript
142.251.155.119
Google LLC
General
Full URL
https://www.google.com/js/th/4pMmjwvOS2kjRCXjDCV7i2J4CsXNLQ2vv-HF0yIf4DU.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.155.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
e293268f0bce4b69234425e30c257b8b62780ac5cd2d0dafbfe1c5d3221fe035
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
78140
report-to
{"group":"botguard-scs","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/botguard-scs"}]}
x-content-type-options
nosniff
expires
Thu, 30 Sep 2027 21:14:46 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 30 Sep 2026 21:14:46 GMT
last-modified
Mon, 28 Sep 2026 10:30:00 GMT
content-type
text/javascript
vary
Accept-Encoding
cache-control
public, max-age=31536000
cross-origin-opener-policy
same-origin; report-to="botguard-scs"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/botguard-scs
accept-ranges
bytes
content-length
24187
x-xss-protection
0
server
sffe
GET
H3
200
4pMmjwvOS2kjRCXjDCV7i2J4CsXNLQ2vv-HF0yIf4DU.js Show response
www.google.com/js/th/ Frame 8D10
61 KB
0
0ms
0ms
Script
text/javascript
142.251.155.119
Google LLC
General
Full URL
https://www.google.com/js/th/4pMmjwvOS2kjRCXjDCV7i2J4CsXNLQ2vv-HF0yIf4DU.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.155.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
e293268f0bce4b69234425e30c257b8b62780ac5cd2d0dafbfe1c5d3221fe035
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
78140
report-to
{"group":"botguard-scs","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/botguard-scs"}]}
x-content-type-options
nosniff
expires
Thu, 30 Sep 2027 21:14:46 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 30 Sep 2026 21:14:46 GMT
last-modified
Mon, 28 Sep 2026 10:30:00 GMT
content-type
text/javascript
vary
Accept-Encoding
cache-control
public, max-age=31536000
cross-origin-opener-policy
same-origin; report-to="botguard-scs"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/botguard-scs
accept-ranges
bytes
content-length
24187
x-xss-protection
0
server
sffe
GET
H3
200
id Show response
googleads.g.doubleclick.net/pagead/ Frame B420
113 B
159 B
77ms
62ms
XHR
application/json
142.251.110.154
Google LLC
General
Full URL
https://googleads.g.doubleclick.net/pagead/id
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.110.154 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f154.1e100.net
Software
cafe /
Resource Hash
4a57458a371fef2adfea0c00928aaf1a47a827c53bfa6ba23e6026177271ecaf
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
date
Thu, 01 Oct 2026 18:57:06 GMT
content-type
application/json; charset=UTF-8
content-disposition
attachment; filename="f.txt"
cache-control
no-cache, no-store, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
access-control-allow-origin
https://www.youtube.com
content-length
133
x-xss-protection
0
server
cafe
GET
H2
200
ad_status.js Show response
static.doubleclick.net/instream/ Frame B420
29 B
0
0ms
0ms
Script
text/javascript
2a00:1450:4001:c15::95
Google LLC
General
Full URL
https://static.doubleclick.net/instream/ad_status.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a00:1450:4001:c15::95 Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
eed0dc1fdb5d97ed188ae16fd5e1024a5bb744af47340346be2146300a6c54b9
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://www.youtube.com/

Response headers

age
782
report-to
{"group":"ads-doubleclick-media","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/ads-doubleclick-media"}]}
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 18:59:03 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 18:44:03 GMT
last-modified
Thu, 12 Dec 2013 23:40:16 GMT
content-type
text/javascript
cache-control
public, max-age=900
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to="ads-doubleclick-media"
content-length
29
x-xss-protection
0
server
sffe
GET
H3
200
m=r78Drb Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/ck=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/exm=base,root/excm=base,root/ed=1/br=1/rs=AGKMywESyf9Y9X87KVWSKj1IXnBDyFL... Frame B420
914 KB
0
0ms
0ms
Script
text/javascript
142.251.154.4
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/ck=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/exm=base,root/excm=base,root/ed=1/br=1/rs=AGKMywESyf9Y9X87KVWSKj1IXnBDyFLpDQ/m=r78Drb
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.154.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
ca01e9635150b32eea34bab004744a814e45a564585eeb9a572af2120e9091c4
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://www.youtube.com/embed/_1W51TfwOEA?enablejsapi=1

Response headers

content-encoding
br
age
22072
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 12:49:13 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 12:49:13 GMT
last-modified
Wed, 30 Sep 2026 19:08:25 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
226102
x-xss-protection
0
server
sffe
GET
H2
200
ibs:dpid=963840&dpuuid=9c1a0b31-7301-41fb-8f2a-844137adf9ca
dpm.demdex.net/ Frame 0222
Redirect Chain
  • https://playerservices.live.streamtheworld.com/api/getuuid?redir=https%3A%2F%2Fdpm.demdex.net%2Fibs%3Adpid%3D963840%26dpuuid%3D%40UUID%40
  • https://dpm.demdex.net/ibs:dpid=963840&dpuuid=9c1a0b31-7301-41fb-8f2a-844137adf9ca
42 B
703 B
50ms
49ms
Image
image/gif
52.17.233.147
Amazon.com
General
Full URL
https://dpm.demdex.net/ibs:dpid=963840&dpuuid=9c1a0b31-7301-41fb-8f2a-844137adf9ca
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Server
52.17.233.147 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-52-17-233-147.eu-west-1.compute.amazonaws.com
Software
/
Resource Hash
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Content-Type-Options nosniff

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
Referer
https://prisacom.demdex.net/

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
no-cache,no-store,must-revalidate,max-age=0,proxy-revalidate,no-transform,private
dcs
dcs-prod-irl1-1-v097-0deea9b4f.edge-irl1.demdex.com 2 ms
content-encoding
zstd
pragma
no-cache
x-content-type-options
nosniff
x-tid
anSuRROj4lc=
expires
Thu, 01 Jan 1970 00:00:00 UTC
content-length
46
p3p
policyref="/w3c/p3p.xml", CP="NOI NID CURa ADMa DEVa PSAa PSDa OUR SAMa BUS PUR COM NAV INT"
date
Thu, 01 Oct 2026 18:57:06 GMT
content-type
image/gif

Redirect headers

location
https://dpm.demdex.net/ibs:dpid=963840&dpuuid=9c1a0b31-7301-41fb-8f2a-844137adf9ca
x-stw-site
PAR
connection
close
access-control-allow-credentials
true
access-control-allow-origin
*
p3p
policyref="http://tds.media.streamtheworld.com/w3c/policy/tds-p3p.xml", CP="NOI DSP COR ADM PSAo PSDo OURo SAMo UNRo OTRo BUS COM NAV DEM STA PRE"
date
Thu, 01 Oct 2026 18:57:06 GMT
content-language
de-CH
GET
H3
200
m=cwx9N Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/ck=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/exm=base,r78Drb,root/excm=base,root/ed=1/br=1/rs=AGKMywESyf9Y9X87KVWSKj1I... Frame CCE2
60 KB
0
0ms
0ms
Script
text/javascript
142.251.155.119
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/ck=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/exm=base,r78Drb,root/excm=base,root/ed=1/br=1/rs=AGKMywESyf9Y9X87KVWSKj1IXnBDyFLpDQ/m=cwx9N
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.155.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
a4a51f4bfe4bd295d2a57cb9a791fa3a5749f45b3d3ae05b518dfc410883650e
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/s3a4OQR-10M?enablejsapi=1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
21600
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 12:57:05 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 12:57:05 GMT
last-modified
Wed, 30 Sep 2026 19:08:25 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
15913
x-xss-protection
0
server
sffe
GET
H3
200
m=cwx9N Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/ck=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/exm=base,r78Drb,root/excm=base,root/ed=1/br=1/rs=AGKMywESyf9Y9X87KVWSKj1I... Frame 8D10
60 KB
0
0ms
0ms
Script
text/javascript
142.251.155.119
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/ck=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/exm=base,r78Drb,root/excm=base,root/ed=1/br=1/rs=AGKMywESyf9Y9X87KVWSKj1IXnBDyFLpDQ/m=cwx9N
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.155.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
a4a51f4bfe4bd295d2a57cb9a791fa3a5749f45b3d3ae05b518dfc410883650e
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/fRIhCiUVaKs?enablejsapi=1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
21600
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 12:57:05 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 12:57:05 GMT
last-modified
Wed, 30 Sep 2026 19:08:25 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
15913
x-xss-protection
0
server
sffe
GET
H3
200
4pMmjwvOS2kjRCXjDCV7i2J4CsXNLQ2vv-HF0yIf4DU.js Show response
www.google.com/js/th/ Frame B420
61 KB
0
0ms
0ms
Script
text/javascript
142.251.155.119
Google LLC
General
Full URL
https://www.google.com/js/th/4pMmjwvOS2kjRCXjDCV7i2J4CsXNLQ2vv-HF0yIf4DU.js
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.155.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
e293268f0bce4b69234425e30c257b8b62780ac5cd2d0dafbfe1c5d3221fe035
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

Referer
https://www.youtube.com/

Response headers

content-encoding
br
age
78140
report-to
{"group":"botguard-scs","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/botguard-scs"}]}
x-content-type-options
nosniff
expires
Thu, 30 Sep 2027 21:14:46 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 30 Sep 2026 21:14:46 GMT
last-modified
Mon, 28 Sep 2026 10:30:00 GMT
content-type
text/javascript
vary
Accept-Encoding
cache-control
public, max-age=31536000
cross-origin-opener-policy
same-origin; report-to="botguard-scs"
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/botguard-scs
accept-ranges
bytes
content-length
24187
x-xss-protection
0
server
sffe
GET
H3
200
m=cwx9N Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/ck=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/exm=base,r78Drb,root/excm=base,root/ed=1/br=1/rs=AGKMywESyf9Y9X87KVWSKj1I... Frame B420
60 KB
0
0ms
0ms
Script
text/javascript
142.251.155.119
Google LLC
General
Full URL
https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/ck=ytembeds.base.qzDvqMbGmKI.L.W.O/am=AAAAQA/d=1/exm=base,r78Drb,root/excm=base,root/ed=1/br=1/rs=AGKMywESyf9Y9X87KVWSKj1IXnBDyFLpDQ/m=cwx9N
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.155.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
a4a51f4bfe4bd295d2a57cb9a791fa3a5749f45b3d3ae05b518dfc410883650e
Security Headers
Name Value
Content-Security-Policy require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/_1W51TfwOEA?enablejsapi=1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
21600
report-to
{"group":"youtube-main-app-web-scs-key","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube-main-app-web-scs-key"}]}
x-content-type-options
nosniff
expires
Fri, 01 Oct 2027 12:57:05 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 12:57:05 GMT
last-modified
Wed, 30 Sep 2026 19:08:25 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-security-policy
require-trusted-types-for 'script'; report-uri https://csp.withgoogle.com/csp/youtube-main-app-web-scs-key
cache-control
public, max-age=31536000
timing-allow-origin
*youtube.com
cross-origin-opener-policy
same-origin; report-to="youtube-main-app-web-scs-key"
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
content-length
15913
x-xss-protection
0
server
sffe
GET
H2
200
default.jpg
i.ytimg.com/vi/s3a4OQR-10M/ Frame CCE2
3 KB
0
0ms
0ms
Image
image/jpeg
2a00:1450:4001:c25::77
Google LLC
General
Full URL
https://i.ytimg.com/vi/s3a4OQR-10M/default.jpg
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/s3a4OQR-10M?enablejsapi=1
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a00:1450:4001:c25::77 Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
4e450e74a3d680d3ff2de1ebd994eee8d653c336c8260b50059d5c1e0123d522
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

etag
"1756912348"
age
2453
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 20:16:12 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 18:16:12 GMT
content-type
image/jpeg
cache-control
public, max-age=7200
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
2707
x-xss-protection
0
server
sffe
GET
H2
200
sddefault.jpg
i.ytimg.com/vi/fRIhCiUVaKs/ Frame 8D10
29 KB
0
0ms
0ms
Image
image/jpeg
2a00:1450:4001:c25::77
Google LLC
General
Full URL
https://i.ytimg.com/vi/fRIhCiUVaKs/sddefault.jpg
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/fRIhCiUVaKs?enablejsapi=1
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a00:1450:4001:c25::77 Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
01fa6f87fff322f56611bd5393de9caa4c7d7b6a92a040d2f2cee6249147af5f
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

etag
"1786055734"
age
66
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 20:55:59 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Thu, 01 Oct 2026 18:55:59 GMT
content-type
image/jpeg
cache-control
public, max-age=7200
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
accept-ranges
bytes
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
30037
x-xss-protection
0
server
sffe
GET
H2
200
default.webp
i.ytimg.com/vi_webp/_1W51TfwOEA/ Frame B420
1 KB
0
0ms
0ms
Image
image/webp
2a00:1450:4001:c25::77
Google LLC
General
Full URL
https://i.ytimg.com/vi_webp/_1W51TfwOEA/default.webp
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/embed/_1W51TfwOEA?enablejsapi=1
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
2a00:1450:4001:c25::77 Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
90e4b6619a37d75bbc2ee6a09bc664d93d559a6ada4c43591d940e47c03ebf6a
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
public, max-age=7200
etag
"1780345100"
cross-origin-resource-policy
cross-origin
report-to
{"group":"youtube","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/youtube"}]}
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 20:57:05 GMT
accept-ranges
bytes
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cross-origin-opener-policy-report-only
same-origin; report-to="youtube"
content-length
1220
date
Thu, 01 Oct 2026 18:57:05 GMT
x-xss-protection
0
content-type
image/webp
vary
Origin
server
sffe
GET
H2
200
s25198357165255
smetrics.los40.com.pa/b/ss/prisacomglobal/1/JS-2.22.4-LGU4/
43 B
332 B
38ms
36ms
Image
image/gif
63.140.62.120
Amazon.com
General
Full URL
https://smetrics.los40.com.pa/b/ss/prisacomglobal/1/JS-2.22.4-LGU4/s25198357165255?AQB=1&ndh=1&pf=1&t=1%2F9%2F2026%2020%3A57%3A7%204%20-120&sdid=42452EAADA136949-7DE4ED14767231C2&mid=70586572863888596102702472168040448371&aamlh=6&ce=UTF-8&ns=prisacom&cdp=3&pageName=los40compa%2F&g=https%3A%2F%2Flos40.com.pa%2F&c.&getValOnce=3.0&getVisitNum=4.2&.c&cc=EUR&ch=home&server=los40.com.pa&events=event2&aamb=RKhpRz8krg2tLO6pguXWp5olkAcUniQYPHaMWWgdJ3xzPWQmdj0y&v1=D%3Dg&h1=D%3Dc18%2B%22%3E%22%2Bc19%2B%22%3E%22%2Bc20%2B%22%3E%22%2Bc1%2B%22%3E%22pageName&c3=portada&v3=D%3DpageName&v4=D%3Dch&c5=D%3Dg&v7=D%3Dc3&c13=los40_panama&v13=D%3Dc13&c17=web&v17=D%3Dc17&c19=los40pa&v19=D%3Dc19&c20=los40.com.pa&v20=D%3Dc20&v22=anonimo&v27=https%3A%2F%2Flos40.com.pa%2F&c28=1&v28=D%3Dc28&c31=musical&v31=1790880960661_4734081&c34=70586572863888596102702472168040448371&c42=anonimo&v43=D%3Dc34&c45=LOS40%20Panam%C3%A1%3A%20noticias%20musicales%20y%20todos%20los%20%C3%A9xitos&v45=LOS40%20Panam%C3%A1%3A%20noticias%20musicales%20y%20todos%20los%20%C3%A9xitos&c47=panama&v47=D%3Dc47&c49=not-set&v49=D%3Dc49&c50=arc&v50=D%3Dc50&c53=https%3A%2F%2Flos40.com.pa%2F&v53=D%3Dc53&v55=not-set&c61=los40&v61=D%3Dc61&v62=D%3Dc31&c66=secuencial&v66=D%3Dc66&v81=D%3Dmid&v92=anonimo&v101=launch-los40-6.0.19&v102=2.22.4&v104=smetrics.los40.com.pa&v105=no-needed&v112=not-set&s=1600x1200&c=24&j=1.6&v=N&k=Y&bw=1600&bh=1200&mcorgid=2387401053DB208C0A490D4C%40AdobeOrg&AQE=1
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
63.140.62.120 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ip-63-140-62-120.data.adobedc.net
Software
jag /
Resource Hash
a1ecbaed793a1f564c49c671f2dd0ce36f858534ef6d26b55783a06b884cc506
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Content-Type-Options nosniff
X-Xss-Protection 1; mode=block

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
no-cache, no-store, max-age=0, no-transform, private
pragma
no-cache
etag
3845887721471737856-4613752055098913756
x-content-type-options
nosniff
expires
Wed, 30 Sep 2026 18:57:07 GMT
access-control-allow-origin
*
p3p
CP="This is not a P3P policy"
content-length
43
date
Thu, 01 Oct 2026 18:57:07 GMT
x-xss-protection
1; mode=block
last-modified
Fri, 02 Oct 2026 18:57:07 GMT
vary
*
server
jag
content-type
image/gif;charset=utf-8
GET
H2
200
radio-api-live-broadcast Show response
los40.com.pa/pf/api/v3/content/fetch/
4 KB
0
1ms
0ms
Fetch
application/json
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/api/v3/content/fetch/radio-api-live-broadcast?query=%7B%22radioStationId%22%3A%22025000%22%2C%22date%22%3A%222026-10-01T20%253A57%253A00%252B02%253A00%22%2C%22itemsPerPage%22%3A3%2C%22imageCutCode%22%3A%22Rec_720x720%22%2C%22emissionType%22%3A%22Normal%22%7D&d=1025
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/pf/resources/js/libs/persistent-player.min.js?d=1025&mxId=00000000
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
85869fb973a1806ba200cb3ff2a7f51f69eca3b8c15c0850956bd3fa445c64d4
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
Accept
application/json
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-security-policy
upgrade-insecure-requests
cache-control
max-age=3600
content-encoding
gzip
x-arc-ttl
3600
etag
W/"105e-B1yGRV+i5osUYOz1kQInf+e5tSA"
x-arc-pb-request-id
346ce16a-28cc-4591-9abb-25c8686bd02f
expires
Thu, 01 Oct 2026 19:57:06 GMT
content-length
833
date
Thu, 01 Oct 2026 18:57:06 GMT
x-arc-request-id
0.b2163017.1790881026.64a5
content-type
application/json; charset=utf-8
vary
Accept-Encoding
server
openresty
last-modified
Thu, 01 Oct 2026 18:57:06 GMT
GET
H2
200
radio-api-cross-podcasts Show response
los40.com.pa/pf/api/v3/content/fetch/
3 KB
2 KB
208ms
207ms
Fetch
application/json
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/api/v3/content/fetch/radio-api-cross-podcasts?query=%7B%22id%22%3A%22efcf2926-2d1d-5b09-8741-4bb3dc257348%22%2C%22accountName%22%3A%22los40%22%7D&d=1025
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/pf/resources/js/libs/persistent-player.min.js?d=1025&mxId=00000000
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
bcf032fc780ca203640744f771fe4a1b076786c01b46eb5a087a6949e5ca5b41
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
Accept
application/json
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-security-policy
upgrade-insecure-requests
cache-control
max-age=57
content-encoding
gzip
x-arc-ttl
600
etag
W/"c14-cAsEqaHDVAvLWopMGcTZIA4Ep5c"
x-arc-pb-request-id
27e7679d-5873-423d-aa9e-a59681f68a74
expires
Thu, 01 Oct 2026 18:58:04 GMT
content-length
1304
date
Thu, 01 Oct 2026 18:57:07 GMT
x-arc-request-id
0.b2163017.1790881027.6928
content-type
application/json; charset=utf-8
vary
Accept-Encoding
server
openresty
last-modified
Thu, 01 Oct 2026 18:48:04 GMT
GET
H2
200
010006518771.png
recursosweb.prisaradio.com/fotos/original/
12 MB
12 MB
84ms
24ms
Image
image/png
199.232.198.133
Fastly
General
Full URL
https://recursosweb.prisaradio.com/fotos/original/010006518771.png
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
199.232.198.133 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
AmazonS3 /
Resource Hash
143f8b3775ba1b6628971459b36f6e47f9df6a3b0bf79871fbb7f98c11507253

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

etag
"b6a05120c609445dc519eabbfd5f33f4-2"
age
857
x-amz-storage-class
STANDARD_IA
x-cache
HIT, HIT
date
Thu, 01 Oct 2026 18:57:07 GMT
last-modified
Thu, 01 Oct 2026 13:34:15 GMT
x-served-by
cache-lhr-egll1980074-LHR, cache-lin1730050-LIN
x-cache-hits
12, 0
content-type
image/png
x-timer
S1790881027.130001,VS0,VE2
via
1.1 varnish, 1.1 varnish
x-amz-meta-gs-mod-t
2026-10-01T10:28:43.000Z
accept-ranges
bytes
access-control-allow-origin
*
content-length
12327032
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H3
204
generate_204
www.youtube.com/ Frame CCE2
0
11 B
18ms
18ms
Image
text/plain
142.251.155.119
Google LLC
General
Full URL
https://www.youtube.com/generate_204?fAZxVQ
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.155.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/s3a4OQR-10M?enablejsapi=1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
0
date
Thu, 01 Oct 2026 18:57:07 GMT
cross-origin-resource-policy
cross-origin
GET
H3
204
generate_204
www.youtube.com/ Frame 8D10
0
11 B
17ms
17ms
Image
text/plain
142.251.155.119
Google LLC
General
Full URL
https://www.youtube.com/generate_204?IuVzCQ
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.155.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/fRIhCiUVaKs?enablejsapi=1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
0
date
Thu, 01 Oct 2026 18:57:07 GMT
cross-origin-resource-policy
cross-origin
GET
H2
200
010006518770.jpg
recursosweb.prisaradio.com/fotos/original/
53 KB
54 KB
58ms
58ms
Image
image/jpeg
199.232.198.133
Fastly
General
Full URL
https://recursosweb.prisaradio.com/fotos/original/010006518770.jpg
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
199.232.198.133 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
AmazonS3 /
Resource Hash
f3fba6fde0798f18cb49b903a15a0de3678c57ebaecab19bfaac0c684e4e7d39

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

etag
"3a61eb3750b79562af7b78863ba22214"
age
857
x-amz-storage-class
STANDARD_IA
x-cache
HIT, HIT
date
Thu, 01 Oct 2026 18:57:07 GMT
last-modified
Thu, 01 Oct 2026 13:34:12 GMT
x-served-by
cache-lhr-egll1980035-LHR, cache-lin1730050-LIN
x-cache-hits
10, 0
content-type
image/jpeg
x-timer
S1790881027.141021,VS0,VE2
via
1.1 varnish, 1.1 varnish
x-amz-meta-gs-mod-t
2026-10-01T10:24:54.000Z
accept-ranges
bytes
access-control-allow-origin
*
content-length
54772
server
AmazonS3
x-amz-server-side-encryption
AES256
GET
H2
200
010006518008.png
recursosweb.prisaradio.com/fotos/original/
451 KB
451 KB
58ms
58ms
Image
image/png
199.232.198.133
Fastly
General
Full URL
https://recursosweb.prisaradio.com/fotos/original/010006518008.png
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H2
Security
TLS 1.2, ECDHE_RSA, AES_128_GCM
Server
199.232.198.133 , United States, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
AmazonS3 /
Resource Hash
8280b6a55e0d394c314e318b5411fa280a3d1c44cd024d66a369139d55d42354

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

etag
"566eec7ccfaf63f489292138fc4be59b"
age
857
x-amz-storage-class
STANDARD_IA
x-cache
HIT, HIT
date
Thu, 01 Oct 2026 18:57:07 GMT
last-modified
Tue, 29 Sep 2026 14:04:43 GMT
x-served-by
cache-lhr-egwu1540030-LHR, cache-lin1730050-LIN
x-cache-hits
9, 0
content-type
image/png
x-timer
S1790881027.141018,VS0,VE2
via
1.1 varnish, 1.1 varnish
x-amz-meta-gs-mod-t
2026-09-29T11:16:52.000Z
accept-ranges
bytes
access-control-allow-origin
*
content-length
461538
server
AmazonS3
x-amz-server-side-encryption
AES256
POST
H3
200
GenerateIT Show response
jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/ Frame CCE2
94 B
137 B
39ms
37ms
XHR
application/json+protobuf
172.217.113.4
Google LLC
General
Full URL
https://jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/GenerateIT
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H3
Security
QUIC, , AES_256_GCM
Server
172.217.113.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
d84a739ec087affcee58e153035fe7589b9228b978454f4a91ab091df1ce5f37
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

X-Goog-Api-Key
AIzaSyDyT5W0Jh49F30Pqqtyfdf7pDLFKLJoAnw
sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
Content-Type
application/json+protobuf
sec-ch-ua-mobile
?0

Response headers

access-control-expose-headers
vary,vary,vary,content-encoding,date,server,content-length
content-encoding
gzip
access-control-allow-credentials
true
x-content-type-options
nosniff
access-control-allow-origin
https://www.youtube.com
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
114
date
Thu, 01 Oct 2026 18:57:07 GMT
x-xss-protection
0
content-type
application/json+protobuf; charset=UTF-8
vary
Origin, X-Origin, Referer
server
ESF
x-frame-options
SAMEORIGIN
POST
H3
200
GenerateIT Show response
jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/ Frame 8D10
94 B
137 B
42ms
41ms
XHR
application/json+protobuf
172.217.113.4
Google LLC
General
Full URL
https://jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/GenerateIT
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H3
Security
QUIC, , AES_256_GCM
Server
172.217.113.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
94d6bbbf99047bd31493a9d2c23c6e9d4abc7bae96f408f0fe04518bf05449ca
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

X-Goog-Api-Key
AIzaSyDyT5W0Jh49F30Pqqtyfdf7pDLFKLJoAnw
sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
Content-Type
application/json+protobuf
sec-ch-ua-mobile
?0

Response headers

access-control-expose-headers
vary,vary,vary,content-encoding,date,server,content-length
content-encoding
gzip
access-control-allow-credentials
true
x-content-type-options
nosniff
access-control-allow-origin
https://www.youtube.com
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
114
date
Thu, 01 Oct 2026 18:57:07 GMT
x-xss-protection
0
content-type
application/json+protobuf; charset=UTF-8
vary
Origin, X-Origin, Referer
server
ESF
x-frame-options
SAMEORIGIN
GET
H3
204
generate_204
www.youtube.com/ Frame B420
0
11 B
17ms
16ms
Image
text/plain
142.251.155.119
Google LLC
General
Full URL
https://www.youtube.com/generate_204?Y5BG6Q
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.155.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
/
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/embed/_1W51TfwOEA?enablejsapi=1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
0
date
Thu, 01 Oct 2026 18:57:07 GMT
cross-origin-resource-policy
cross-origin
POST
H3
200
GenerateIT Show response
jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/ Frame B420
94 B
137 B
36ms
35ms
XHR
application/json+protobuf
172.217.113.4
Google LLC
General
Full URL
https://jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/GenerateIT
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H3
Security
QUIC, , AES_256_GCM
Server
172.217.113.4 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
ESF /
Resource Hash
2c7e6adc17ee675c286506792d1e49b90a7136bacf19501d95bd7e260ba2d87a
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

X-Goog-Api-Key
AIzaSyDyT5W0Jh49F30Pqqtyfdf7pDLFKLJoAnw
sec-ch-ua-platform
"Linux"
Referer
https://www.youtube.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
Content-Type
application/json+protobuf
sec-ch-ua-mobile
?0

Response headers

access-control-expose-headers
vary,vary,vary,content-encoding,date,server,content-length
content-encoding
gzip
access-control-allow-credentials
true
x-content-type-options
nosniff
access-control-allow-origin
https://www.youtube.com
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
114
date
Thu, 01 Oct 2026 18:57:07 GMT
x-xss-protection
0
content-type
application/json+protobuf; charset=UTF-8
vary
Origin, X-Origin, Referer
server
ESF
x-frame-options
SAMEORIGIN
GET
H2
200
ima3.js Show response
imasdk.googleapis.com/js/sdkloader/
496 KB
155 KB
128ms
67ms
Script
text/javascript
2a00:1450:4001:c0f::5f
Google LLC
General
Full URL
https://imasdk.googleapis.com/js/sdkloader/ima3.js
Requested by
Host: sdk.listenlive.co
URL: https://sdk.listenlive.co/web/2.9/td-sdk.min.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a00:1450:4001:c0f::5f Frankfurt am Main, Germany, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
cafe /
Resource Hash
70e413f998f220ce0372b62c87b71bd692619a6ea7f10413a009341e3b60dd24
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
etag
14296416696992859845
x-content-type-options
nosniff
expires
Thu, 01 Oct 2026 18:57:07 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
date
Thu, 01 Oct 2026 18:57:07 GMT
content-type
text/javascript; charset=UTF-8
vary
Accept-Encoding
content-disposition
attachment; filename="f.txt"
cache-control
private, max-age=900, stale-while-revalidate=3600
timing-allow-origin
*
cross-origin-resource-policy
cross-origin
access-control-allow-origin
*
content-length
158666
x-xss-protection
0
server
cafe
GET
H2
404
site-service Show response
los40.com.pa/pf/api/v3/content/fetch/
9 B
309 B
216ms
216ms
Fetch
text/plain
2a02:26f0:3500:12::1730:178a
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com.pa/pf/api/v3/content/fetch/site-service?query=%7B%22sectionIds%22%3A%22%2Fcadena-ser%22%7D&d=1025
Requested by
Host: los40.com.pa
URL: https://los40.com.pa/pf/resources/dist/js/main.js?d=1025&mxId=00000000
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:178a Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
openresty /
Resource Hash
0019dfc4b32d63c1392aa264aed2253c1e0c2fb09216f8e2cc269bbfb8bb49b5
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-security-policy
upgrade-insecure-requests
cache-control
max-age=120
x-arc-ttl
-1
etag
W/"9-0gXL1ngzMqISxa6S1zx3F4wtLyg"
x-arc-pb-request-id
0add0247-7de3-4600-ab24-02cca0ed538d
expires
Thu, 01 Oct 2026 18:59:08 GMT
content-length
9
date
Thu, 01 Oct 2026 18:57:08 GMT
x-arc-request-id
0.b2163017.1790881028.70ff
content-type
text/plain; charset=utf-8
last-modified
Thu, 01 Oct 2026 18:57:08 GMT
server
openresty
GET
H2
200
https%3A%2F%2Flos40es00.epimg.net%2Ffavicon.png
los40.com/resizer/v2/
331 B
683 B
54ms
54ms
Other
image/gif
2a02:26f0:3500:12::1730:1799
AKAMAI-ASN1 Akama...
General
Full URL
https://los40.com/resizer/v2/https%3A%2F%2Flos40es00.epimg.net%2Ffavicon.png?auth=a7681bb4fb5b0fd8645fa1d2798f065218a9acb2bce1608dea252d9b67fe91a2&quality=70&smart=true
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2a02:26f0:3500:12::1730:1799 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
Software
Akamai Image Manager /
Resource Hash
f8c960272fb620dedbef9d09b719c97ed8392f12dbcb501292392920f62aaeb4
Security Headers
Name Value
Content-Security-Policy upgrade-insecure-requests, upgrade-insecure-requests

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://los40.com.pa/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

mpulse_cdn_cache
HIT
content-security-policy
upgrade-insecure-requests, upgrade-insecure-requests
cache-control
private, no-transform, max-age=31407289
x-arc-ttl
31536000
etag
"57376ff3-c3d"
mpulse_origin_time
0
expires
Thu, 30 Sep 2027 07:11:57 GMT
content-length
331
x-serial
257
date
Thu, 01 Oct 2026 18:57:08 GMT
last-modified
Wed, 30 Sep 2026 07:11:56 GMT
content-type
image/gif
server
Akamai Image Manager
x-arc-request-id
0.99163017.1790881028.184b3997
POST
H3
200
log_event Show response
www.youtube.com/youtubei/v1/ Frame CCE2
28 B
51 B
39ms
35ms
XHR
application/json
142.251.155.119
Google LLC
General
Full URL
https://www.youtube.com/youtubei/v1/log_event?alt=json
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.155.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
scaffolding on HTTPServer2 /
Resource Hash
d7d5e54ad1e33d7ab49c664323ced79cb9723ff15e9764cd0edc3e15208e8336
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0
X-YouTube-Client-Name
56
X-YouTube-Ad-Signals
dt=1790881026423&flash=0&frm=2&u_tz=120&u_his=1&u_h=1200&u_w=1600&u_ah=1200&u_aw=1600&u_cd=24&bc=31&bih=-12245933&biw=-12245933&brdim=1570%2C1170%2C1570%2C1170%2C1600%2C0%2C1600%2C1200%2C0%2C0&vis=1&wgl=true&ca_type=image&bid=ANyPxKpitR5nIAtpn4Tjlt85JaoGy6N5aR3a3ER0EZiRbtDaoKSWa0pjMJu5MPQzvCh01N50VWterFCQt_BAK6P0c7opoYnbLg
X-Goog-Event-Time
1790881029209
X-YouTube-Client-Version
2.20261001.01.00
Content-Type
application/json
X-YouTube-Page-Label
youtube.embeds.web_20261001_01_RC00
X-YouTube-Page-CL
991486115
X-YouTube-Utc-Offset
120
Referer
https://www.youtube.com/embed/s3a4OQR-10M?enablejsapi=1
X-YouTube-Device
cbr=Chrome&cbrver=154.0.0.0&ceng=WebKit&cengver=537.36&cos=X11&cplatform=DESKTOP
X-Goog-Visitor-Id
CgsweHpDLUo2ZTUxUSiC2vrVBjIKCgJDSBIEGgAgPmLfAgrcAjIyLllUPXd3OHFaTFdsSnJXNWtfamxST3hYdGNOT3hRYWVhWkxONG9Fajllakt3NjF0STQwaHFLWVZDZUtUN1lieTQ4ZTJlX0ZxOGI2akc5VS14ZGFUbUxVRkRobnVKQWRtdndYR3RlZW1Wamp1dzhSRWl0SVlVMzlLTjF1T3ZjOEVaUTBwMXhmdmQ2dEhneHRzSDF5TmNfNFl3Y0h4QThqQW93VWpDN21hMW9GY0t2SDlaR1ZOeEFEb19NVFVuLVFFaFFQSkpoc3VsM3Nuckl4cGxBQ2w0Y0lmUlhibl9lSVQ2ZDFkQ2ZoRUtRLWJwaF9mTFlXbzlKeUd3dFBkT0dsODZqalpOUk1mcnV6NjZGUTZpczQtejhQVUkxalYtNHBNdmU3eWp4Zmdub1Y0QTQydEVTaTkwX3FQYWRZRmlzOG83T2tqWldPdjl5R3NFTll1azNMMkFVNnA1dw%3D%3D
X-Goog-Request-Time
1790881029209
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
X-YouTube-Time-Zone
Europe/Zurich

Response headers

content-encoding
br
x-content-type-options
nosniff
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
31
date
Thu, 01 Oct 2026 18:57:09 GMT
x-xss-protection
0
content-type
application/json; charset=UTF-8
vary
Origin, X-Origin, Referer
server
scaffolding on HTTPServer2
x-frame-options
SAMEORIGIN
POST
H3
200
log_event Show response
www.youtube.com/youtubei/v1/ Frame 8D10
28 B
51 B
38ms
33ms
XHR
application/json
142.251.155.119
Google LLC
General
Full URL
https://www.youtube.com/youtubei/v1/log_event?alt=json
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.155.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
scaffolding on HTTPServer2 /
Resource Hash
d7d5e54ad1e33d7ab49c664323ced79cb9723ff15e9764cd0edc3e15208e8336
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0
X-YouTube-Client-Name
56
X-YouTube-Ad-Signals
dt=1790881026440&flash=0&frm=2&u_tz=120&u_his=1&u_h=1200&u_w=1600&u_ah=1200&u_aw=1600&u_cd=24&bc=31&bih=-12245933&biw=-12245933&brdim=1570%2C1170%2C1570%2C1170%2C1600%2C0%2C1600%2C1200%2C453%2C255&vis=1&wgl=true&ca_type=image&bid=ANyPxKqDTM42MLH7OAjVfvLfFvGsa53o5Y7-v2HeqHLB4XU9upw2JTLatbgchoQXTDQnZJXVsj0M5vP5_1b9eu0MfSOJ0pQ1Pw
X-Goog-Event-Time
1790881029221
X-YouTube-Client-Version
2.20261001.01.00
Content-Type
application/json
X-YouTube-Page-Label
youtube.embeds.web_20261001_01_RC00
X-YouTube-Page-CL
991486115
X-YouTube-Utc-Offset
120
Referer
https://www.youtube.com/embed/fRIhCiUVaKs?enablejsapi=1
X-YouTube-Device
cbr=Chrome&cbrver=154.0.0.0&ceng=WebKit&cengver=537.36&cos=X11&cplatform=DESKTOP
X-Goog-Visitor-Id
CgsweHpDLUo2ZTUxUSiC2vrVBjIKCgJDSBIEGgAgPmLfAgrcAjIyLllUPXd3OHFaTFdsSnJXNWtfamxST3hYdGNOT3hRYWVhWkxONG9Fajllakt3NjF0STQwaHFLWVZDZUtUN1lieTQ4ZTJlX0ZxOGI2akc5VS14ZGFUbUxVRkRobnVKQWRtdndYR3RlZW1Wamp1dzhSRWl0SVlVMzlLTjF1T3ZjOEVaUTBwMXhmdmQ2dEhneHRzSDF5TmNfNFl3Y0h4QThqQW93VWpDN21hMW9GY0t2SDlaR1ZOeEFEb19NVFVuLVFFaFFQSkpoc3VsM3Nuckl4cGxBQ2w0Y0lmUlhibl9lSVQ2ZDFkQ2ZoRUtRLWJwaF9mTFlXbzlKeUd3dFBkT0dsODZqalpOUk1mcnV6NjZGUTZpczQtejhQVUkxalYtNHBNdmU3eWp4Zmdub1Y0QTQydEVTaTkwX3FQYWRZRmlzOG83T2tqWldPdjl5R3NFTll1azNMMkFVNnA1dw%3D%3D
X-Goog-Request-Time
1790881029221
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
X-YouTube-Time-Zone
Europe/Zurich

Response headers

content-encoding
br
x-content-type-options
nosniff
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
31
date
Thu, 01 Oct 2026 18:57:09 GMT
x-xss-protection
0
content-type
application/json; charset=UTF-8
vary
Origin, X-Origin, Referer
server
scaffolding on HTTPServer2
x-frame-options
SAMEORIGIN
POST
H3
200
log_event Show response
www.youtube.com/youtubei/v1/ Frame B420
28 B
51 B
38ms
36ms
XHR
application/json
142.251.155.119
Google LLC
General
Full URL
https://www.youtube.com/youtubei/v1/log_event?alt=json
Requested by
Host: www.youtube.com
URL: https://www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.GRsEQlAF6LQ.2021.O/am=AAAAQA/d=1/excm=base,root/br=1/rs=AGKMywGSCPtH3qy2nAvybufjvKoZB2_bUA/m=root,base
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.155.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
scaffolding on HTTPServer2 /
Resource Hash
d7d5e54ad1e33d7ab49c664323ced79cb9723ff15e9764cd0edc3e15208e8336
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0
X-YouTube-Client-Name
56
X-YouTube-Ad-Signals
dt=1790881026490&flash=0&frm=2&u_tz=120&u_his=1&u_h=1200&u_w=1600&u_ah=1200&u_aw=1600&u_cd=24&bc=31&bih=-12245933&biw=-12245933&brdim=1570%2C1170%2C1570%2C1170%2C1600%2C0%2C1600%2C1200%2C0%2C0&vis=1&wgl=true&ca_type=image&bid=ANyPxKocR2QWCdl3J1BWplqDSw-vb2c3tlbVCuovVbIUlb1LlCngmJu9DpdDYBkBUwXFpWIMvDWz20Lxfkdnq8_kE6mhaWovBg
X-Goog-Event-Time
1790881029253
X-YouTube-Client-Version
2.20261001.01.00
Content-Type
application/json
X-YouTube-Page-Label
youtube.embeds.web_20261001_01_RC00
X-YouTube-Page-CL
991486115
X-YouTube-Utc-Offset
120
Referer
https://www.youtube.com/embed/_1W51TfwOEA?enablejsapi=1
X-YouTube-Device
cbr=Chrome&cbrver=154.0.0.0&ceng=WebKit&cengver=537.36&cos=X11&cplatform=DESKTOP
X-Goog-Visitor-Id
CgsweHpDLUo2ZTUxUSiC2vrVBjIKCgJDSBIEGgAgPmLfAgrcAjIyLllUPXd3OHFaTFdsSnJXNWtfamxST3hYdGNOT3hRYWVhWkxONG9Fajllakt3NjF0STQwaHFLWVZDZUtUN1lieTQ4ZTJlX0ZxOGI2akc5VS14ZGFUbUxVRkRobnVKQWRtdndYR3RlZW1Wamp1dzhSRWl0SVlVMzlLTjF1T3ZjOEVaUTBwMXhmdmQ2dEhneHRzSDF5TmNfNFl3Y0h4QThqQW93VWpDN21hMW9GY0t2SDlaR1ZOeEFEb19NVFVuLVFFaFFQSkpoc3VsM3Nuckl4cGxBQ2w0Y0lmUlhibl9lSVQ2ZDFkQ2ZoRUtRLWJwaF9mTFlXbzlKeUd3dFBkT0dsODZqalpOUk1mcnV6NjZGUTZpczQtejhQVUkxalYtNHBNdmU3eWp4Zmdub1Y0QTQydEVTaTkwX3FQYWRZRmlzOG83T2tqWldPdjl5R3NFTll1azNMMkFVNnA1dw%3D%3D
X-Goog-Request-Time
1790881029253
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
X-YouTube-Time-Zone
Europe/Zurich

Response headers

content-encoding
br
x-content-type-options
nosniff
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
31
date
Thu, 01 Oct 2026 18:57:09 GMT
x-xss-protection
0
content-type
application/json; charset=UTF-8
vary
Origin, X-Origin, Referer
server
scaffolding on HTTPServer2
x-frame-options
SAMEORIGIN

Failed requests

These URLs were requested, but there was no response received. You will also see them in the list above.

Domain
ib.adnxs.com
URL
https://ib.adnxs.com/getuid?https%3A%2F%2Fdpm.demdex.net%2Fibs%3Adpid%3D358%26dpuuid%3D%24UID
Domain
www.youtube.com
URL
https://www.youtube.com/api/stats/atr?ns=yt&el=embedded&cpn=LNKP4ORDQeEME1wp&ver=2&cmt=0&fs=0&rt=0.799&euri=https%3A%2F%2Flos40.com.pa%2F&lact=811&cl=990399410&mos=0&volume=100&cbr=Chrome&cbrver=154.0.0.0&c=WEB_EMBEDDED_PLAYER&cver=2.20261001.01.00&cplayer=UNIPLAYER&cos=X11&cplatform=DESKTOP&epm=1&hl=de_DE&cr=CH&len=268&fexp=v1%2C100673025%2C-76668381%2C27058999%2C34656%2C124674%2C117689%2C9252%2C16509%2C23206%2C35403%2C65299%2C2878%2C12227%2C25059%2C4174%2C30446%2C18706%2C26008%2C13016%2C14665%2C1422%2C6620%2C2784%2C23826%2C9500%2C1840%2C24119%2C70718%2C20589%2C34313%2C9181%2C52983%2C6032%2C1168%2C372%2C7759%2C34320%2C11462%2C26847%2C1353%2C13722%2C4366%2C9716%2C3614%2C26539%2C3844%2C17159%2C1340%2C10904%2C3243%2C2%2C17339%2C9038%2C1537%2C5823%2C20493%2C3%2C12278%2C5673%2C15390%2C15564%2C3307%2C13874%2C3638%2C11%2C5316%2C1326%2C2685%2C3038%2C5469%2C3424%2C12239%2C13293%2C12996&muted=0&docid=s3a4OQR-10M
Domain
www.youtube.com
URL
https://www.youtube.com/youtubei/v1/log_event?alt=json
Domain
www.youtube.com
URL
https://www.youtube.com/api/stats/atr?ns=yt&el=embedded&cpn=KLg7J0qTrBXgfu1y&ver=2&cmt=0&fs=0&rt=0.844&euri=https%3A%2F%2Flos40.com.pa%2F&lact=856&cl=990399410&mos=0&volume=100&cbr=Chrome&cbrver=154.0.0.0&c=WEB_EMBEDDED_PLAYER&cver=2.20261001.01.00&cplayer=UNIPLAYER&cos=X11&cplatform=DESKTOP&epm=1&hl=de_DE&cr=CH&len=226&fexp=v1%2C100673025%2C-76668381%2C494888%2C26564111%2C34656%2C124674%2C117689%2C9252%2C16509%2C23206%2C68547%2C32155%2C2877%2C12228%2C25059%2C4174%2C30447%2C18705%2C26008%2C13015%2C15427%2C661%2C6620%2C897%2C1887%2C23826%2C9500%2C1840%2C24119%2C32527%2C38192%2C20588%2C34313%2C9181%2C32873%2C20110%2C5696%2C336%2C1168%2C372%2C3793%2C3966%2C34320%2C11462%2C26849%2C1351%2C13722%2C4366%2C9716%2C3614%2C10450%2C16089%2C3844%2C17159%2C1339%2C6470%2C4435%2C3241%2C4%2C17339%2C9038%2C1537%2C5824%2C20491%2C2%2C17954%2C15389%2C15564%2C1649%2C1659%2C10935%2C2541%2C398%2C3637%2C11%2C5315%2C1327%2C2686%2C3037%2C2743%2C2726%2C3423%2C12240%2C13292&muted=0&docid=fRIhCiUVaKs
Domain
www.youtube.com
URL
https://www.youtube.com/youtubei/v1/log_event?alt=json
Domain
www.youtube.com
URL
https://www.youtube.com/api/stats/atr?ns=yt&el=embedded&cpn=3eZV6zj1JsoJhf2s&ver=2&cmt=0&fs=0&rt=0.819&euri=https%3A%2F%2Flos40.com.pa%2F&lact=832&cl=990399410&mos=0&volume=100&cbr=Chrome&cbrver=154.0.0.0&c=WEB_EMBEDDED_PLAYER&cver=2.20261001.01.00&cplayer=UNIPLAYER&cos=X11&cplatform=DESKTOP&epm=1&hl=de_DE&cr=CH&len=217&fexp=v1%2C100673025%2C-76668381%2C27058999%2C34656%2C124674%2C117689%2C9252%2C16509%2C23206%2C35405%2C34391%2C30906%2C2878%2C12227%2C25059%2C4174%2C30446%2C18706%2C26008%2C9671%2C3344%2C1192%2C14234%2C662%2C6621%2C2783%2C23826%2C9500%2C1840%2C18113%2C76725%2C20588%2C34313%2C9181%2C32872%2C20111%2C6032%2C191%2C977%2C372%2C7759%2C34320%2C11462%2C26845%2C1354%2C13723%2C4366%2C9716%2C3614%2C26539%2C3843%2C17160%2C1339%2C10905%2C1261%2C1981%2C3%2C17339%2C9037%2C1538%2C5823%2C20492%2C4%2C17951%2C15390%2C15564%2C3308%2C13874%2C3639%2C9%2C5315%2C1327%2C5723%2C5469%2C3424%2C3129%2C1887%2C2860%2C113%2C2746%2C1504%2C13292&muted=0&docid=_1W51TfwOEA
Domain
www.youtube.com
URL
https://www.youtube.com/youtubei/v1/log_event?alt=json

Verdicts & Comments Add Verdict or Comment

166 JavaScript Window variables Go Pro

Only in urlscan Pro

Inspect and pivot on JavaScript variables, identifiers, and other key site metadata data with urlscan Pro. Reveal and search on client-side frameworks, runtime variables, and custom values.
Click for more information
Free trials of urlscan Pro are available.

These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.

object| 0 object| 1 object| 2 object| 3 object| 4 object| 5 object| appData function| d function| n boolean| coreplayer_launcher_loaded function| wichLayerApply number| cmpVersion boolean| gdprAppliesGlobally object| didomiEventListeners object| didomiOnReady function| findAndRemoveYoutubeFromDisabledVendors object| PMUser object| PRISA object| pmuser boolean| PMUserCkLoaded object| DTM boolean| spaLoading object| appContext function| __tcfapi string| GPT_ADUNIT object| GPT_KEYS object| player_permanente object| PERSISTENT_PLAYER object| coreplayer object| core boolean| core_loaded string| core_compilation boolean| isOffsetTimezoneStation boolean| mm_preload_none boolean| mm_ttag string| mm_ttag_val string| tap_banners number| timevideo_ad string| companion_ad_300_250 boolean| ttt29 boolean| mm_geoblock boolean| mm_autoplay object| $CORE function| $PLAYER function| $CONTROLLER function| $SKIN function| $UTIL function| $ADS function| $TAG function| $PLAYERS function| $PLAYERS_ALPHABET function| $CN function| $CONSENT function| $NET function| $HL function| $DATA function| $CACHE function| $IC function| $RC function| $AlPHABET function| $SET_CURRENT_PLAYER function| $CORE_CONF function| $_ALFA function| $_BRAVO function| $_CHARLIE function| $_DELTA function| $_ECHO function| $_FOXTROT object| _satellite boolean| __satelliteLoaded object| adobe function| Visitor object| s_c_il number| s_c_in object| __alloyMonitors function| alloy object| __alloyNS object| __target_telemetry object| ___target_traces function| mboxCreate function| mboxDefine function| mboxUpdate object| didomiVendorListCore object| didomiRemoteConfig string| didomiCountry string| didomiRegion object| didomiGeoRegulations function| Pixel object| besocyPixelScript boolean| MAT_blocked object| dt_spxl_CO function| AppMeasurement_Module_ActivityMap function| AppMeasurement function| s_gi function| s_pgicq number| s_objectID number| s_giq object| s string| url object| digitalData object| webpackChunkDidomi object| Didomi object| DidomiSanitizing boolean| pmSegmentsUpdated function| onYouTubeIframeAPIReady object| apstag object| dataLayer object| googletag object| adsbygoogle object| didomiState object| consentData object| acceptedPurposses object| rejectedPurposses object| enabled_json object| disabled_json object| acceptedVendors object| rejectedVendors object| vendors_enabled_json object| vendors_disabled_json object| process function| perm_musicalesSkin object| scriptUrl object| ttPolicy object| YT object| YTConfig function| onYTReady number| __aps_slice object| _aps boolean| apstagLOADED object| apscustom object| marfeel object| targetTimeLoad function| cookieWrite function| cookieRead string| g object| s_i_prisacomglobal number| currentShowIndex number| live_audio_interval object| now_playing boolean| playeriniciado function| TdPlatform function| TdCompanions object| platform function| lodash function| setImmediate function| clearImmediate function| TDSdk object| _google_rum_ns_ object| google_persistent_state_async number| google_global_correlator object| ggeac object| google_js_reporting_queue function| Goog_AdSense_Lidar_sendVastEvent function| Goog_AdSense_Lidar_getViewability function| Goog_AdSense_Lidar_getUrlSignalsArray function| Goog_AdSense_Lidar_getUrlSignalsList number| google_srt object| google object| module$exports$google3$javascript$ads$interactivemedia$sdk$clientside$api$companion_ad_selection_settings object| module$exports$google3$javascript$ads$interactivemedia$sdk$clientside$api$ad_cue_points object| module$exports$google3$javascript$ads$interactivemedia$sdk$clientside$api$ads_rendering_settings object| ima object| module$exports$google3$javascript$ads$interactivemedia$sdk$clientside$api$ad_error object| module$exports$google3$javascript$ads$interactivemedia$sdk$clientside$api$ad_error_event object| module$exports$google3$javascript$ads$interactivemedia$sdk$clientside$api$ad_event object| module$exports$google3$javascript$ads$interactivemedia$sdk$clientside$api$ads_manager_loaded_event
25 Cookies Go Pro

Only in urlscan Pro

Review, search, and pivot on browser cookies and persistence site data to see how a site tracks users and keeps sessions alive across visits.
Click for more information
Free trials of urlscan Pro are available.

Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.

Domain/Path Expires Name / Value
los40.com.pa/ 1970-01-22
02:13:37
Name: emisoralos40pa_tagname
Value: 40_principales
los40.com.pa/ 1970-01-22
02:13:37
Name: emisoralos40pa_name
Value: LOS40 Panamá
los40.com.pa/ 1970-01-22
02:13:37
Name: emisoralos40pa_tagname_session
Value: 40_principales
los40.com.pa/ 1970-01-22
02:13:37
Name: emisoralos40pa_id
Value: 025000
.youtube.com/ 1969-12-31
23:59:59
Name: YSC
Value: Z4vCRrdCx5Q
.youtube.com/ 1970-01-21
21:47:13
Name: VISITOR_INFO1_LIVE
Value: 0xzC-J6e51Q
.youtube.com/ 1970-01-21
21:47:13
Name: VISITOR_PRIVACY_METADATA
Value: CgJDSBIEGgAgPg%3D%3D
.los40.com.pa/ 1969-12-31
23:59:59
Name: at_check
Value: true
.demdex.net/ 1970-01-21
21:47:13
Name: demdex
Value: 70615015185308116162705257438871360841
.los40.com.pa/ 1969-12-31
23:59:59
Name: AMCVS_2387401053DB208C0A490D4C%40AdobeOrg
Value: 1
los40.com.pa/ 1970-01-22
02:13:37
Name: __bs_id
Value: bs.1.0.BGdiUJ4WGmij
.los40.com.pa/ 1970-01-22
03:04:01
Name: s_ecid
Value: MCMID%7C70586572863888596102702472168040448371
.los40.com.pa/ 1970-01-22
03:04:01
Name: AMCV_2387401053DB208C0A490D4C%40AdobeOrg
Value: 1176715910%7CMCIDTS%7C20728%7CMCMID%7C70586572863888596102702472168040448371%7CMCAAMLH-1791485825%7C6%7CMCAAMB-1791485825%7CRKhpRz8krg2tLO6pguXWp5olkAcUniQYPHaMWWgdJ3xzPWQmdj0y%7CMCOPTOUT-1790888225s%7CNONE%7CMCAID%7CNONE%7CvVersion%7C5.4.0
.los40.com.pa/ 1970-01-22
03:04:01
Name: mbox
Value: session#8cf22a303489402fa3d06cfa2438692f#1790882887|PC#8cf22a303489402fa3d06cfa2438692f.37_0#1854125826
.doubleclick.net/ 1970-01-22
03:04:01
Name: IDE
Value: AHWqTUnym9sm9hY4FII3_umsonq7Ua2cgTIoLJ6tauJ5AeRNCZuHQuav4Q8HxG5V1ag
.youtube.com/ 1970-01-21
21:47:13
Name: __Secure-YNID
Value: 22.YT=ww8qZLWlJrW5k_jlROxXtcNOxQaeaZLN4oEj9ejKw61tI40hqKYVCeKT7Yby48e2e_Fq8b6jG9U-xdaTmLUFDhnuJAdmvwXGteemVjjuw8REitIYU39KN1uOvc8EZQ0p1xfvd6tHgxtsH1yNc_4YwcHxA8jAowUjC7ma1oFcKvH9ZGVNxADo_MTUn-QEhQPJJhsul3snrIxplACl4cIfRXbn_eIT6d1dCfhEKQ-bph_fLYWo9JyGwtPdOGl86jjZNRMfruz66FQ6is4-z8PUI1jV-4pMve7yjxfgnoV4A42tESi90_qPadYFis8o7OkjZWOv9yGsENYuk3L2AU6p5w
.youtube.com/ 1970-01-21
21:47:13
Name: __Secure-ROLLOUT_TOKEN
Value: CI3xsLjiu5alsgEQ0ZXa2r-ZlwMYjMKY27-ZlwM%3D
.los40.com.pa/ 1970-01-22
02:56:49
Name: kndctr_2387401053DB208C0A490D4C_AdobeOrg_identity
Value: CiY3MDU4NjU3Mjg2Mzg4ODU5NjEwMjcwMjQ3MjE2ODA0MDQ0ODM3MVIRCIehz8aPNBgBKgRJUkwxMAPwAYehz8aPNA==
.los40.com.pa/ 1970-01-21
17:28:02
Name: kndctr_2387401053DB208C0A490D4C_AdobeOrg_cluster
Value: irl1
.dpm.demdex.net/ 1970-01-21
21:47:13
Name: dpm
Value: 70615015185308116162705257438871360841
.live.streamtheworld.com/ 1970-01-21
18:11:13
Name: uuid-s
Value: 9c1a0b31-7301-41fb-8f2a-844137adf9ca
.pubmatic.com/ 1970-01-21
17:29:27
Name: KTPCACOOKIE
Value: YES
.pubmatic.com/ 1970-01-22
02:13:37
Name: KADUSERCOOKIE
Value: 2D34D10C-38AF-4AA3-ACA5-B11BDA5E79D1
.demdex.net/ 1970-01-21
21:47:13
Name: dextp
Value: 358-1-1790881025931|771-1-1790881026081|903-1-1790881026188|19566-1-1790881026290|175765-1-1790881026452|963840-1-1790881026581
.los40.com.pa/ 1969-12-31
23:59:59
Name: s_cc
Value: true

16 Console Messages

A page may trigger messages to the console to be logged. These are often error messages about being unable to load a resource or execute a piece of JavaScript. Sometimes they also provide insight into the technology behind a website.

Source Level URL
Text
other warning URL: https://los40.com.pa/(Line 1)
Message:
Unrecognized feature: 'web-share'.
rendering warning URL: https://los40.com.pa/
Message:
[]Automatic fallback to software WebGL has been deprecated. Please use the --enable-unsafe-swiftshader flag to opt in to lower security guarantees for trusted content.
rendering warning URL: https://www.youtube.com/embed/fRIhCiUVaKs
Message:
[]Automatic fallback to software WebGL has been deprecated. Please use the --enable-unsafe-swiftshader flag to opt in to lower security guarantees for trusted content.
rendering warning URL: https://www.youtube.com/embed/_1W51TfwOEA
Message:
[]Automatic fallback to software WebGL has been deprecated. Please use the --enable-unsafe-swiftshader flag to opt in to lower security guarantees for trusted content.
rendering warning URL: https://www.youtube.com/embed/s3a4OQR-10M
Message:
[]Automatic fallback to software WebGL has been deprecated. Please use the --enable-unsafe-swiftshader flag to opt in to lower security guarantees for trusted content.
rendering warning URL: https://www.youtube.com/embed/s3a4OQR-10M
Message:
No available adapters.
rendering warning URL: https://www.youtube.com/embed/fRIhCiUVaKs
Message:
No available adapters.
rendering warning URL: https://www.youtube.com/embed/_1W51TfwOEA
Message:
No available adapters.
network error URL: https://playerservices.live.streamtheworld.com/api/idsync.js?stationId=&gdpr=0&gdpr_consent=undefined&bounce=true
Message:
Failed to load resource: the server responded with a status of 400 (Bad Request)
rendering warning URL: https://www.youtube.com/embed/s3a4OQR-10M?enablejsapi=1
Message:
[]Automatic fallback to software WebGL has been deprecated. Please use the --enable-unsafe-swiftshader flag to opt in to lower security guarantees for trusted content.
rendering warning URL: https://www.youtube.com/embed/fRIhCiUVaKs?enablejsapi=1
Message:
[]Automatic fallback to software WebGL has been deprecated. Please use the --enable-unsafe-swiftshader flag to opt in to lower security guarantees for trusted content.
rendering warning URL: https://www.youtube.com/embed/_1W51TfwOEA?enablejsapi=1
Message:
[]Automatic fallback to software WebGL has been deprecated. Please use the --enable-unsafe-swiftshader flag to opt in to lower security guarantees for trusted content.
rendering warning URL: https://www.youtube.com/embed/s3a4OQR-10M?enablejsapi=1
Message:
No available adapters.
rendering warning URL: https://www.youtube.com/embed/fRIhCiUVaKs?enablejsapi=1
Message:
No available adapters.
rendering warning URL: https://www.youtube.com/embed/_1W51TfwOEA?enablejsapi=1
Message:
No available adapters.
network error URL: https://los40.com.pa/pf/api/v3/content/fetch/site-service?query=%7B%22sectionIds%22%3A%22%2Fcadena-ser%22%7D&d=1025
Message:
Failed to load resource: the server responded with a status of 404 ()

Security Headers

This page lists any security headers set by the main page. If you want to understand what these mean and how to use them, head on over to this page

Header Value
Content-Security-Policy upgrade-insecure-requests

Indicators

This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.

adobedc.demdex.net
assets.adobedtm.com
c.amazon-adsystem.com
cm.g.doubleclick.net
cmp.prisa.com
config.aps.amazon-adsystem.com
dcs.adobedc.net
dpm.demdex.net
edge.adobedc.net
fapi-top.prisasd.com
fonts.gstatic.com
googleads.g.doubleclick.net
i.ytimg.com
ib.adnxs.com
image6.pubmatic.com
imasdk.googleapis.com
jnn-pa.googleapis.com
los40.com
los40.com.pa
match.adsrvr.org
pagead2.googlesyndication.com
player.prisamedia.com
playerservices.live.streamtheworld.com
prisacom.demdex.net
prisacom.tt.omtrdc.net
prra.spxl.socy.es
recursosweb.prisaradio.com
sdk.listenlive.co
sdk.privacy-center.org
smetrics.los40.com.pa
static.doubleclick.net
static.prisa.com
synchroscript.deliveryengine.adswizz.com
www.google.com
www.youtube.com
ib.adnxs.com
www.youtube.com
103.231.98.107
142.251.110.154
142.251.110.94
142.251.14.155
142.251.14.156
142.251.154.4
142.251.155.119
172.217.113.4
178.33.150.172
18.238.243.129
18.245.46.103
192.173.31.109
199.232.198.133
2001:4860:4826:400::
2001:4860:482b:400::
2001:4860:4841:400::
2600:9000:20ab:ea00:1:ef39:a380:93a1
2600:9000:28eb:1000:5:b7cc:d3c0:93a1
2a00:1450:4001:c0f::5f
2a00:1450:4001:c15::95
2a00:1450:4001:c25::77
2a02:26f0:2780:a9e::1e80
2a02:26f0:3500:12::1730:178a
2a02:26f0:3500:12::1730:1799
3.173.128.89
3.174.46.14
35.71.131.137
51.138.12.100
52.17.233.147
52.30.159.196
63.140.62.120
63.140.62.139
63.140.62.200
63.140.62.210
0019dfc4b32d63c1392aa264aed2253c1e0c2fb09216f8e2cc269bbfb8bb49b5
005bf06762a807e300c8a79da4100f20f6184910b22f1d702aafc112efb4bb77
00df653296a4836407e88e03794a222fd8701a823752c35f025ca4fabf7b4b48
00e0c89c0f922c98de0de5d4b3f359ca5995a269f8d74831f6ecb79d6ef1b916
00f5a7dd994f87d2312bafc45ea100e7901d6259aac1858b1d7eaaa069e7ea1e
01fa6f87fff322f56611bd5393de9caa4c7d7b6a92a040d2f2cee6249147af5f
02afbc3f8f6c9db03cb2053aec2dac67d4835891273da81ef6fd34d8949071c4
038e94abcde149f32572693ff5883e880c4f08a63df56f27ea8eeefdb329a753
06b99248a163333e36980a6cfb756f1a7de60fa49517162b87b1a44d5d48f844
08eaed4a37f8ae323b8a0faf40ade34714604fd86825ecc0453fb0c71efc6fd3
09d4ace821999277a3db65e31a074ae22b628dd21100cdb4a37127a8e291631b
0aa0f96f7bd97efa74470d5d766aebc7f1892c1b3a27326b02567754ee3fbb08
1022bdddc3d32541a12cc7856a51b713e92ffd50ae0691f826a5418a366f54b5
1056d0181c72eb0d725f840073cbbb5b66a3fdf5926bb70d0ac1096018772ccf
143f8b3775ba1b6628971459b36f6e47f9df6a3b0bf79871fbb7f98c11507253
16be8fac20dcb1b8cf7e819d449cc10adb5b9919eaacb5d68c019536aec55648
1b2755ef1cd36503c1c9b048ddf83eda7feb1bbf691bb26f277029f6a876f896
1c548847d5707fe6e7c95c678c0ad5a72b53e4e4000fdb1a49eae49dbe64528c
20b535fa80c8189e3b87d1803038389960203a886d502bc2ef1857affc2f38d2
20d31559e45ce5462a4dd4e20410e48dc28798967f7bced6740439e5a350ee3f
20eac260aebb8b85588427d391542e2577bca60a773dbea3dcecd1154761a85e
2405c568804ff70ec4366ff13f20dc1adbd8acdce151e8a57784765656095ce9
248cc827d02e70984c52df2fa3f261eca39f6d3c0a8a24a37f4a407ee4d8d337
25e85111d31c7b43a4c54ef0ae7865aee1adf2908b7522fc90463fc232eb93bf
2755d9f1441bb50077d6db548a0a9188f095b12619741e5db452e9c02beebcd4
29dafeba1ea69519e201f76e76ba1a7fb508554c443e33792ea4e48a4369e5e2
2c7e6adc17ee675c286506792d1e49b90a7136bacf19501d95bd7e260ba2d87a
2d15b52e43fa02423bc0b9ba6f7987de39c81c4f53392554bd3332af5c60dab3
3024e387751b683c51e63b3a5b0cbe521795b1dcff0e495cf438211f5205c32d
3053e145611a5994e86254654465ab2692aaedb3af72ffa04452aa39ffdbc799
31b2631f7b0931b746105ed464b2469bae130674907729c58554d4e9b259847c
33980143bfbab156ea95543a0982dc303283902811f193dcb20a94ce55411021
3598ed32f0f6fec1accc27e8d084f15cf77a451ddf649cae9be98b0da1d8b0f4
3718414c79ddd99304d70bf93704327a8b20b02fa45bf36a907fea538830555e
386f61f76f2fd4164c973cfe038be172b139aea6b8d36d1c10ad9177a3f94052
39da84904cb9b1c7179ab587e50a28037066fc25f4c494b9f10c6c8710c7ee4c
3c9902065d76c2e9cf04e2d7555f6a3e2ff55f17f2956e3389dbdc836ff15d31
3dc9dbaedcce7656d7e5f2121902728ed4327d1f0f197a10d90e4f219ed6c738
41971663d4fa9fac35327285ca4844983efbfea78c68335f4885f7d5e8d45aa2
41a24c8fc108a45fab4d2fef4ecc666678cc5f2958664a27ae8aa2fa1d7fa651
42ca9ca6df9f1ce73546272c990ee1475ca10c0032d814e08910c08ba6b990da
43c743fa5a31cb96055d7933b5ef59a7cdcf22724de1ebdc162304ef3289b9e9
43f040f22fdc551d207513b8e2b7be100273ff01f221dbdbb95e0d3cee9ba2b8
462a66acbf50e933685e7587e9f1441df8225b2bb4d6b7bc5e757eccf4ff6575
4a57458a371fef2adfea0c00928aaf1a47a827c53bfa6ba23e6026177271ecaf
4b8a762bf1f92cafdc2400a4aa5fb13d9dc649999406ecc5c24ec6d28c0994ae
4e450e74a3d680d3ff2de1ebd994eee8d653c336c8260b50059d5c1e0123d522
501cda4917af84bbaf002d6b53d606403fe7a2a5549a596d680249f9d8cc10bc
516fce352bd44ae4987e9ee4cb538fced0ccad0ea7d26743320a3875337190e2
5228e2d37779820e50e291ac069ec397f6712df232452640a9210a6fd91a9cc7
53bea1615bdbda079c26a285ec2c2c96fdcfd2fc6d6eb22a435ac9278a967a8b
5834080f39b7a4b2110cde1b11997cc54163b79b350de478daffb713717e9b32
5b275c116242b1da62a2f7e05ee653d88a6d94e3ba3e65a34d6368274e9f20c9
5c49f23c1aa61273f0426906fdf87115f14eff7c0e783b44551e9fce03f7431e
5cbb53b20b48230acf93104dfb18edcce5abeb39cf59999c1b8910d2c3f23142
5feb6ccd9965ded425e1e8d2bd1797ab9740d592d47f23cb84740dc8169d58ee
60486887aff825b8083b9f9bbd60a7c994bee63e7de6775bd2afd596e6fe3e97
622131b4cece767db3c86041482e1103b5b90ed911333d08e04c6c4af55c4da3
62f672d6a1e7408e0d1806bc80ced1f939c4bd054d0d8216f4842c15c16bb01d
62ffc2a6642875e95ce9c8e75eac2c4320d32be120823e5d807b757e4d72e73d
655a13e81cc47eb28c0b40b85f014519f3032021817e1579145ca879c9309fcf
657aaec2cfe6fc02cbdf55326617378d9b813702d4fe6d1d330e7d92ee4450ac
68f1b808fa4dc0c3104b1dc2bffadc6517167840a3b0f9dd9ac0011d4cec0cec
6b8708480876814fcce40a6aad216e047a2f780a3a958bd8d9261c68b131f5e7
6c84b666d4df1743ad060633775e7d7caf97c85fb28a84f55a9c3eeb6e090b5e
6ee0adbb8e4fb539be973f11b0c979bbb3e19f1e21bbb84df5e54a9760973e20
6f190eeb69a176008b5f453480c482c64ba9538a0a6b46eefcb0fb3197ad20f4
70a06dcb720f594a598a01fcfdd7769a1178076f803d61d3da7efab4384f5141
70e413f998f220ce0372b62c87b71bd692619a6ea7f10413a009341e3b60dd24
73636f1d6c2d28f48d82ddc0c4a77d397a6acc9ed2b7b014d03f717c4c3e406e
746545703d9d979d390b0e042dcec5134b82c94247e69c5f6dbf50094d38e015
769b47f6cb38895551a44b064e4afd8f7e13bb9ec15bda07443cfcd10e20c150
7bea17a80a61ed0f54248b4ffc4c718f7c8ff2619742577a73591d62ce074da8
7c63466de3d85a30131cfc8ca195ae5b839883c2f4dcf5bad4ca3265fa4ae076
8280b6a55e0d394c314e318b5411fa280a3d1c44cd024d66a369139d55d42354
8494b27686c18de5dc85774c56197edd88739bdbf11535b591323749af7aca80
84da29e74152c5f3bb82157c74c24304090541c602ded4207d9e9e18b7283dbd
85869fb973a1806ba200cb3ff2a7f51f69eca3b8c15c0850956bd3fa445c64d4
896b02fd97d42f7620cd2c9e5fc1b16c64b447469fd6df06747bf283028e7784
8976b88cd7b0fac9110721d5ee1e0471111cf8b313616541a5a1bf7b773742f3
89dec1f10ed0da63883beaa22f8476b4ace5a0709a7a5cdea8fcb3d6bb38172e
8a3eb03ff1cddcb8cf9bedf5b93c288e515bb55c5df8add5e283efb2d7099851
8d70b3e6badb6973663b398d297bb32eaedd08826a1af98d0a1cfce5324ffce0
90e4b6619a37d75bbc2ee6a09bc664d93d559a6ada4c43591d940e47c03ebf6a
91f11824da56ff57eb156e208f66929898d919f9fcc60789a4670cf9755db30d
9219086b4f2c3bf77854b2e06ccd97ad32b9b7a140e65ff8b974a3bae6c7854c
9267ab0d5c68cc8fab1244238f7380df07f70052660f3953e876bb20e4e1e3f0
94d6bbbf99047bd31493a9d2c23c6e9d4abc7bae96f408f0fe04518bf05449ca
966aa4cc84973eff8c83b4013c6e58dd9bfe06a2e8ad88b68e5c938c84fde4ff
a1ecbaed793a1f564c49c671f2dd0ce36f858534ef6d26b55783a06b884cc506
a48033ab8dbf9f974469ec1285b2317c398a9250a4d0467e3ac7e993a055b157
a4a51f4bfe4bd295d2a57cb9a791fa3a5749f45b3d3ae05b518dfc410883650e
a51d1ed6ffaf3d965e806f7b1ef10a337c4378c7b5f0e3be38b6956b35661c05
a55ed8ebc054d8632fd0afb1b06f43c47f5b4d18842303fb109076aecefbd03f
aaea1928868e3ef330ab5278134bac85bd1074b1bb9ac4fa40159fb906b25557
b27c23322be7fc48ca63848b2024c7910a462a6702d9f54fe921f50a5f161422
b4dc09cc9d3cabc8fee6b934540492133215f1ed9bfaf07310316386956cd93d
b4f1713861ee9b24b143a5bc92172c5aaf9af76e8406593516551177d0843d5f
b7aa1d267416afc8f3a744dd935be2fbf102e0dedc767582bfb404cfdd9017f5
ba0973764311004cc5ff9f86b80bd10881e90057c7c0f2716bbbfb08cd35a373
ba6730bccf913770e4062dfa49fab7fff5320146296a9d34a8795ea74c579551
bcf032fc780ca203640744f771fe4a1b076786c01b46eb5a087a6949e5ca5b41
bda621fbe7c839069883292a99bbd863f226600faf1a62b971e045c629141b5a
c1935ffb200277c95a9eca8348b29f1c7dbf0e2b548ab9fb6585f259b0b89bb6
c1cb67546b0fedd9ece25b45e7ada8ee0f85d6c02a35865139f4bddfa3eca6d2
c2dcf46501a48a87a7859596834012e81569a181f7b80bda4d91b04798f84751
c6a6b60c1bcd1083c32e2d1809b4d91a699d6072aa42e612626ecc8977757aa5
c772f5f94c822468df599d6fce72a4b8921390f5fb49b39d7ea6d57492209d7b
ca01e9635150b32eea34bab004744a814e45a564585eeb9a572af2120e9091c4
cc730a79aad4de1ffe9b8ab9fa59daeed7c82ad02a3cc54a4c692a0243a488af
cf0423cf281ce89ea32e234549d2055f6c19b0d982aa3f8c3b147070f49e24fd
d1d39a41576fc9baacb643f6f26beb557215f5d8fd2297171eefc6b3685d1ef7
d231df6f9389398eec75616710dc53dd64315a69dfdfebaaa2cbf0f824a0c456
d2ec536529cfefef0eab6453e615717281a7a52ab0a099767315b87c441f9ef5
d37b5f9b60958395c3cab7207c76ed40d7fc4d9b6efe9f942f7461500cf9cccf
d4541ccc650611057ee03ca66fe00a75120ccb64b539302b772c7753c1ce6675
d4f23126c68b19daf5da6627ce56905644a3cc06f634a576428cf7095e923d26
d5e6ce5d020856b27b56efd756d0e313a4f6177adec408e1cf7dbebe70cea90a
d7d5e54ad1e33d7ab49c664323ced79cb9723ff15e9764cd0edc3e15208e8336
d84a739ec087affcee58e153035fe7589b9228b978454f4a91ab091df1ce5f37
d9f120ed9ded67f4ac4db35c78e4683e05a7bea813e91edf6771f95e41f068e0
db37415538fa6f3279331fc6ae11a7839a953e6aed04717013658ede7ad224e3
db6ad205995da14e082e8522a7a82ca52aa824efdb0cad8dadbabf5ffca2faf1
dcc3f3a7421178e332078eebd53f187ba58159e706b3ddb19613d0ce89d882f0
e293268f0bce4b69234425e30c257b8b62780ac5cd2d0dafbfe1c5d3221fe035
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
e5920add0f05bf998d8605cbd92fe34a5aaf0bad21d312a67cbf10288442e7b2
e621e327dec0160361efd7f426a172ca2bdf6d6c07dc1c4b866357d93ca8f1c6
eb47d1409ae84e69d57499f00ed9b17fed8549ae4a1cf508385037a15adfa6ca
eb97074105525e11e271010800282a6462ea1c17605019b1a5b09c235ec733bc
ecd3bcd411bcfdc529beaa8281bb796f35572e3a3b6329cf34717f886fab9efc
ecd9eeb6d9f743ef01d482ca7d9f9b8c49d1fa8d1bd9043a8866d4f476658585
eed0dc1fdb5d97ed188ae16fd5e1024a5bb744af47340346be2146300a6c54b9
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
f07f071b0126a21c1b964a9bae42ee4c6e2279ab4a695b79a8bd60c5ede849b3
f1451e046925e9b7adad6c742d5c9c7e1bcdacb9387dbe4869615f8b93e83cf1
f3fba6fde0798f18cb49b903a15a0de3678c57ebaecab19bfaac0c684e4e7d39
f5c302502fb11d97d13043e834e5c2b934bb54b61d0989685c2dc27287452e96
f81388d87f85f3c9057669770eff0c3b992d135d7eda537d0804a996e178be80
f8c960272fb620dedbef9d09b719c97ed8392f12dbcb501292392920f62aaeb4
fc8a1209662da01173b39d81a8cbd9c37eee64fd6d927f471006148f0b7dac9a
feb61f57061c97d1a775d1aee86665ae9d3a705c9a384da8980829450e8a4260
fee20f0ab7f9cf7681ff58e4107507c475c9c9c2a8204de11eead6da23a3356c
ff40dc96cdd64de6e3890158055fff059e9e6256bdc0c4be719ad1e079bcdb4d