Summary

This website contacted 38 IPs in 6 countries across 34 domains to perform 148 HTTP transactions. The main IP is 172.67.155.237, located in Ascension Island and belongs to CLOUDFLARENET - Cloudflare, Inc., US. The main domain is daftarslotterpercayaidn.com. 4yr old
TLS certificate: Issued by YE2 on October 7th 2026. Valid for: 3mo.
This is the only time daftarslotterpercayaidn.com was scanned on urlscan.io!

Domain & IP information

IP Address AS Autonomous System
3 172.67.155.237 172.67.155.237 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
1 18.64.211.102 18.64.211.102 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
7 104.19.147.8 104.19.147.8 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
2 3.161.82.109 3.161.82.109 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
2 162.159.133.61 162.159.133.61 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
1 35.186.249.72 35.186.249.72 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC)
1 216.239.32.178 216.239.32.178 15169 (GOOGLE) (GOOGLE - Google LLC)
5 57.144.244.128 57.144.244.128 32934 (FACEBOOK) (FACEBOOK - Facebook)
19 34.117.1.79 34.117.1.79 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC)
5 34.107.218.251 34.107.218.251 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC)
1 7 142.251.13.154 142.251.13.154 15169 (GOOGLE) (GOOGLE - Google LLC)
1 108.138.26.69 108.138.26.69 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
5 18.64.211.128 18.64.211.128 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
4 192.178.183.97 192.178.183.97 15169 (GOOGLE) (GOOGLE - Google LLC)
3 188.114.97.3 188.114.97.3 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
1 18.66.122.124 18.66.122.124 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 178.128.116.123 178.128.116.123 14061 (DIGITALOC...) (DIGITALOCEAN-ASN - DigitalOcean)
8 172.66.0.227 172.66.0.227 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
1 18.66.102.77 18.66.102.77 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
3 104.16.80.73 104.16.80.73 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare)
8 3.161.82.25 3.161.82.25 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
1 9 142.251.156.119 142.251.156.119 15169 (GOOGLE) (GOOGLE - Google LLC)
6 142.251.110.94 142.251.110.94 15169 (GOOGLE) (GOOGLE - Google LLC)
1 216.239.34.36 216.239.34.36 15169 (GOOGLE) (GOOGLE - Google LLC)
1 45.43.142.8 45.43.142.8 16276 (OVH OVH SAS) (OVH OVH SAS)
1 146.75.120.157 146.75.120.157 54113 (FASTLY) (FASTLY - Fastly)
6 142.251.14.157 142.251.14.157 15169 (GOOGLE) (GOOGLE - Google LLC)
2 5 103.132.192.30 103.132.192.30 138552 (RTBHOUSE-...) (RTBHOUSE-AS-AP - RTB HOUSE PTE. LTD.)
1 18.66.147.45 18.66.147.45 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
6 92.123.104.175 92.123.104.175 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.)
1 142.251.127.149 142.251.127.149 15169 (GOOGLE) (GOOGLE - Google LLC)
6 142.251.157.119 142.251.157.119 15169 (GOOGLE) (GOOGLE - Google LLC)
1 35.244.195.172 35.244.195.172 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC)
1 34.193.159.151 34.193.159.151 14618 (AMAZON-AES) (AMAZON-AES - Amazon.com)
1 57.144.244.1 57.144.244.1 32934 (FACEBOOK) (FACEBOOK - Facebook)
1 2.16.10.92 2.16.10.92 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.)
2 63.34.183.36 63.34.183.36 16509 (AMAZON-02) (AMAZON-02 - Amazon.com)
148 38
Apex Domain
Subdomains
Transfer
19 static-src.com
www.static-src.com — Cisco Umbrella Rank: 183958 10yr old
374 KB
15 google.com 1 redirects
www.google.com — Cisco Umbrella Rank: 3 14yr old
3 KB
13 doubleclick.net 1 redirects
googleads.g.doubleclick.net — Cisco Umbrella Rank: 66 10yr old
td.doubleclick.net — Cisco Umbrella Rank: 25184 4yr old
ad.doubleclick.net — Cisco Umbrella Rank: 135 10yr old
25 KB
10 moengage.com
cdn.moengage.com — Cisco Umbrella Rank: 13594 10yr old
sdk-01.moengage.com — Cisco Umbrella Rank: 6562 6yr old
168 KB
7 crazyegg.com
script.crazyegg.com — Cisco Umbrella Rank: 3254 12yr old
114 KB
6 tiktok.com
analytics.tiktok.com — Cisco Umbrella Rank: 680 7yr old
161 KB
6 google.pl
www.google.pl — Cisco Umbrella Rank: 29840 10yr old
995 B
5 creativecdn.com 2 redirects
asia.creativecdn.com — Cisco Umbrella Rank: 14905 10yr old
2 KB
5 flixcar.com
media.flixcar.com — Cisco Umbrella Rank: 23744 12yr old
336 KB
5 visualwebsiteoptimizer.com
dev.visualwebsiteoptimizer.com — Cisco Umbrella Rank: 2740 10yr old
136 KB
5 facebook.net
connect.facebook.net — Cisco Umbrella Rank: 215 14yr old
360 KB
4 twitter.com
analytics.twitter.com — Cisco Umbrella Rank: 1192 10yr old
3 KB
4 t.co
t.co — Cisco Umbrella Rank: 1212 14yr old
2 KB
4 googletagmanager.com
www.googletagmanager.com — Cisco Umbrella Rank: 44 14yr old
683 KB
3 cloudflareinsights.com
static.cloudflareinsights.com — Cisco Umbrella Rank: 291 7yr old
33 KB
3 meubelkayumurah.pics
meubelkayumurah.pics — Cisco Umbrella Rank: 98809 4yr old
23 KB
3 daftarslotterpercayaidn.com
daftarslotterpercayaidn.com 4yr old
98 KB
2 flix360.com
rt.flix360.com — Cisco Umbrella Rank: 36348 10yr old
323 B
2 o-s.io
c.o-s.io — Cisco Umbrella Rank: 100417 9yr old
t.o-s.io — Cisco Umbrella Rank: 55230 9yr old
8 KB
2 google-analytics.com
www.google-analytics.com — Cisco Umbrella Rank: 82 14yr old
region1.google-analytics.com — Cisco Umbrella Rank: 3673 5yr old
21 KB
2 useinsider.com
blibli.api.useinsider.com — Cisco Umbrella Rank: 456296 7yr old
531 B
1 tiktokw.us
analytics-ipv6.tiktokw.us — Cisco Umbrella Rank: 1135 3yr old
984 B
1 facebook.com
www.facebook.com — Cisco Umbrella Rank: 136 12yr old
20 B
1 on.aws
dv-c3e594c6d429469e90b54478358619c3.ecs.us-east-1.on.aws — Cisco Umbrella Rank: 8740 9mo old
1 ads-twitter.com
static.ads-twitter.com — Cisco Umbrella Rank: 1353 10yr old
17 KB
1 co.com
i.ibb.co.com — Cisco Umbrella Rank: 77146 3yr old
170 KB
1 crwdcntrl.net
tags.crwdcntrl.net — Cisco Umbrella Rank: 1099 14yr old
20 KB
1 blackmolesamp.com
gen.blackmolesamp.com — Cisco Umbrella Rank: 679648 4mo old
3 MB
1 flixfacts.com
media.flixfacts.com — Cisco Umbrella Rank: 26700 12yr old
6 KB
1 flix360.io
prod.flixgvid.flix360.io — Cisco Umbrella Rank: 342299 6yr old
360 B
1 googleadservices.com
www.googleadservices.com — Cisco Umbrella Rank: 110 14yr old
3 KB
1 impactcdn.com
utt.impactcdn.com — Cisco Umbrella Rank: 4695 6yr old
24 KB
1 appsflyer.com
websdk.appsflyer.com — Cisco Umbrella Rank: 8680 7yr old
17 KB
0 blibli.com Failed
www.blibli.com Failed 14yr old
148 34
Domain Requested by
19 www.static-src.com daftarslotterpercayaidn.com
www.static-src.com
15 www.google.com 1 redirects daftarslotterpercayaidn.com
www.googletagmanager.com
td.doubleclick.net
8 sdk-01.moengage.com cdn.moengage.com
7 script.crazyegg.com daftarslotterpercayaidn.com
script.crazyegg.com
www.googletagmanager.com
6 analytics.tiktok.com daftarslotterpercayaidn.com
analytics.tiktok.com
6 td.doubleclick.net daftarslotterpercayaidn.com
6 www.google.pl daftarslotterpercayaidn.com
6 googleads.g.doubleclick.net 1 redirects daftarslotterpercayaidn.com
5 asia.creativecdn.com 2 redirects daftarslotterpercayaidn.com
5 media.flixcar.com daftarslotterpercayaidn.com
media.flixfacts.com
media.flixcar.com
5 dev.visualwebsiteoptimizer.com daftarslotterpercayaidn.com
5 connect.facebook.net daftarslotterpercayaidn.com
connect.facebook.net
4 analytics.twitter.com daftarslotterpercayaidn.com
4 t.co daftarslotterpercayaidn.com
4 www.googletagmanager.com daftarslotterpercayaidn.com
www.googletagmanager.com
3 static.cloudflareinsights.com daftarslotterpercayaidn.com
3 meubelkayumurah.pics daftarslotterpercayaidn.com
3 daftarslotterpercayaidn.com daftarslotterpercayaidn.com
static.cloudflareinsights.com
2 rt.flix360.com daftarslotterpercayaidn.com
2 blibli.api.useinsider.com daftarslotterpercayaidn.com
2 cdn.moengage.com daftarslotterpercayaidn.com
1 analytics-ipv6.tiktokw.us analytics.tiktok.com
1 www.facebook.com daftarslotterpercayaidn.com
1 dv-c3e594c6d429469e90b54478358619c3.ecs.us-east-1.on.aws connect.facebook.net
1 t.o-s.io daftarslotterpercayaidn.com
1 ad.doubleclick.net www.googletagmanager.com
1 c.o-s.io daftarslotterpercayaidn.com
1 static.ads-twitter.com daftarslotterpercayaidn.com
1 i.ibb.co.com www.static-src.com
1 region1.google-analytics.com www.googletagmanager.com
1 tags.crwdcntrl.net daftarslotterpercayaidn.com
1 gen.blackmolesamp.com daftarslotterpercayaidn.com
1 media.flixfacts.com daftarslotterpercayaidn.com
1 prod.flixgvid.flix360.io daftarslotterpercayaidn.com
1 www.googleadservices.com daftarslotterpercayaidn.com
1 www.google-analytics.com daftarslotterpercayaidn.com
1 utt.impactcdn.com daftarslotterpercayaidn.com
1 websdk.appsflyer.com daftarslotterpercayaidn.com
0 www.blibli.com Failed daftarslotterpercayaidn.com
148 39

This site contains links to these domains. Also see Links.

Domain
www.google.com
Subject Issuer Validity Valid
daftarslotterpercayaidn.com
YE2
2026-10-07 -
2027-01-05
3mo crt.sh
*.appsflyer.com
Amazon RSA 2048 M01
2025-12-04 -
2027-01-01
1yr crt.sh
script.crazyegg.com
WE1
2026-09-08 -
2026-12-07
3mo crt.sh
*.moengage.com
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2026-01-13 -
2027-02-13
1yr crt.sh
useinsider.com
WE1
2026-08-15 -
2026-11-13
3mo crt.sh
*.impactcdn.com
WR3
2026-09-12 -
2026-12-11
3mo crt.sh
*.google-analytics.com
WE2
2026-09-18 -
2026-12-11
3mo crt.sh
*.facebook.com
DigiCert Global G2 TLS RSA SHA256 2020 CA1
2026-07-16 -
2026-10-14
3mo crt.sh
static-src.com
YR1
2026-09-16 -
2026-12-15
3mo crt.sh
*.visualwebsiteoptimizer.com
WR3
2026-09-29 -
2026-12-28
3mo crt.sh
*.g.doubleclick.net
WE2
2026-09-18 -
2026-12-11
3mo crt.sh
flixgvid.flix360.io
Amazon RSA 2048 M04
2025-12-24 -
2027-01-21
1yr crt.sh
*.flixcar.com
Amazon RSA 2048 M01
2026-10-05 -
2027-04-20
7mo crt.sh
meubelkayumurah.pics
WE1
2026-09-06 -
2026-12-05
3mo crt.sh
*.flixfacts.com
Amazon RSA 2048 M01
2026-10-05 -
2027-04-20
7mo crt.sh
gen.blackmolesamp.com
YE1
2026-08-30 -
2026-11-28
3mo crt.sh
t.co
YE2
2026-09-06 -
2026-12-05
3mo crt.sh
*.twitter.com
YR1
2026-09-28 -
2026-12-27
3mo crt.sh
*.crwdcntrl.net
Amazon RSA 2048 M04
2026-07-10 -
2027-01-23
7mo crt.sh
cloudflareinsights.com
WE1
2026-08-14 -
2026-11-12
3mo crt.sh
*.google.com
WE2
2026-09-18 -
2026-12-11
3mo crt.sh
*.google.pl
WE2
2026-09-18 -
2026-12-11
3mo crt.sh
ibb.co
YE1
2026-08-12 -
2026-11-10
3mo crt.sh
ads-twitter.com
YR2
2026-09-14 -
2026-12-13
3mo crt.sh
*.doubleclick.net
WE2
2026-09-18 -
2026-12-11
3mo crt.sh
*.creativecdn.com
RapidSSL TLS RSA CA G1
2026-09-28 -
2027-04-14
7mo crt.sh
*.o-s.io
Sectigo Public Server Authentication CA OV R36
2026-08-21 -
2027-03-07
7mo crt.sh
*.tiktok.com
RapidSSL TLS ECC CA G1
2026-05-19 -
2026-12-03
7mo crt.sh
dv-c3e594c6d429469e90b54478358619c3.ecs.us-east-1.on.aws
Amazon ECDSA 256 M04
2026-06-12 -
2026-12-26
7mo crt.sh
*.tiktokw.us
RapidSSL TLS ECC CA G1
2026-06-09 -
2026-12-24
7mo crt.sh
flix360.com
Amazon RSA 2048 M04
2026-09-08 -
2027-03-24
7mo crt.sh

This page contains 11 frames:

Primary Page: https://daftarslotterpercayaidn.com/
Frame ID: 3D866D9DCFFE78506FA92F93C10D7727
Requests: 130 HTTP requests in this frame

Frame: https://td.doubleclick.net/td/rul/880395410?random=1726498671571&cv=11&fst=1726498671571&fmt=3&bg=ffffff&guid=ON&async=1&gtm=45je4990v877689920z8810058345za200zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FmetaData%3D4eHyfurj4yL7Q4Ucv84uGYHJb0g2t%2BFdwECMb3QsHNjtAqmaWkaBfGgt5w9qTEikAP03CsR8aLRQodyhRwzA9w%3D%3D%26pickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Online%20Mall%20Blibli.com%2C%20Sensasi%20Belanja%20Online%20Shop%20ala%20Mall&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=event%3Dgtag.config
Frame ID: 75DEA3EB87BE840E2CE36142F154E7E2
Requests: 2 HTTP requests in this frame

Frame: https://asia.creativecdn.com/tags?id=pr_FAOiA95ZI30AXifJGDUt_offer_NUT-60023-01292-00001&id=pr_FAOiA95ZI30AXifJGDUt_uid_unknown&tc=1
Frame ID: CC017A4D2FF0FB4B0209ABB1211188D3
Requests: 1 HTTP requests in this frame

Frame: https://td.doubleclick.net/td/rul/925089264?random=1726498673524&cv=11&fst=1726498673524&fmt=3&bg=ffffff&guid=ON&async=1&gtm=45be4990z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=ecomm_pagetype%3Dproduct%3Becomm_prodid%3DNUT-60023-01292%3Becomm_totalvalue%3D343900
Frame ID: 79233D2DC0816881924C315379F25CE7
Requests: 2 HTTP requests in this frame

Frame: https://td.doubleclick.net/td/rul/920334631?random=1726498673536&cv=11&fst=1726498673536&fmt=3&bg=ffffff&guid=ON&async=1&gtm=45be4990z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=ecomm_pagetype%3Dretail-product-detail%3Becomm_prodid%3DNUT-60023-01292%3Becomm_totalvalue%3D343900
Frame ID: A7791741CA7F4D78774BA60923E828BB
Requests: 2 HTTP requests in this frame

Frame: https://td.doubleclick.net/td/rul/880395410?random=1726498673589&cv=11&fst=1726498673589&fmt=3&bg=ffffff&guid=ON&async=1&gtm=45be4990v877689920z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&label=hEx3CKjo-eADEJKJ56MD&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&value=0&bttype=purchase&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&capi=1&ct_cookie_present=0
Frame ID: B6F7356875C15230726B6755E21A99A5
Requests: 2 HTTP requests in this frame

Frame: https://asia.creativecdn.com/tags?id=pr_FAOiA95ZI30AXifJGDUt_offer_NUT-60023-01292-00001&id=pr_FAOiA95ZI30AXifJGDUt_uid_unknown&tc=1
Frame ID: EDD6465C83FDF5FB0741F1AC66BDF124
Requests: 1 HTTP requests in this frame

Frame: https://td.doubleclick.net/td/rul/925089264?random=1726498714047&cv=11&fst=1726498714047&fmt=3&bg=ffffff&guid=ON&async=1&gtm=45be4990z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1024&u_h=824&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=ecomm_pagetype%3Dproduct%3Becomm_prodid%3DNUT-60023-01292%3Becomm_totalvalue%3D343900
Frame ID: 9998C6CD783843DF0C85CBBD5A335C47
Requests: 2 HTTP requests in this frame

Frame: https://td.doubleclick.net/td/rul/920334631?random=1726498714059&cv=11&fst=1726498714059&fmt=3&bg=ffffff&guid=ON&async=1&gtm=45be4990z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1024&u_h=824&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=ecomm_pagetype%3Dretail-product-detail%3Becomm_prodid%3DNUT-60023-01292%3Becomm_totalvalue%3D343900
Frame ID: AA01E0F3563CA50F20331DB1905A5152
Requests: 2 HTTP requests in this frame

Frame: https://www.facebook.com/tr/
Frame ID: 2CF37718DCD42D4B4C42DDB44748374D
Requests: 1 HTTP requests in this frame

Frame: https://asia.creativecdn.com/tags?id=pr_FAOiA95ZI30AXifJGDUt_home&id=pr_FAOiA95ZI30AXifJGDUt_uid_unknown
Frame ID: CE51214F7C333AFAA1E0C86869B0135E
Requests: 1 HTTP requests in this frame

Screenshot Go Pro

Only in urlscan Pro

Use the Visual Search feature to find pages with visually similar screenshots.
Click for more information
Free trials of urlscan Pro are available.

Page Title

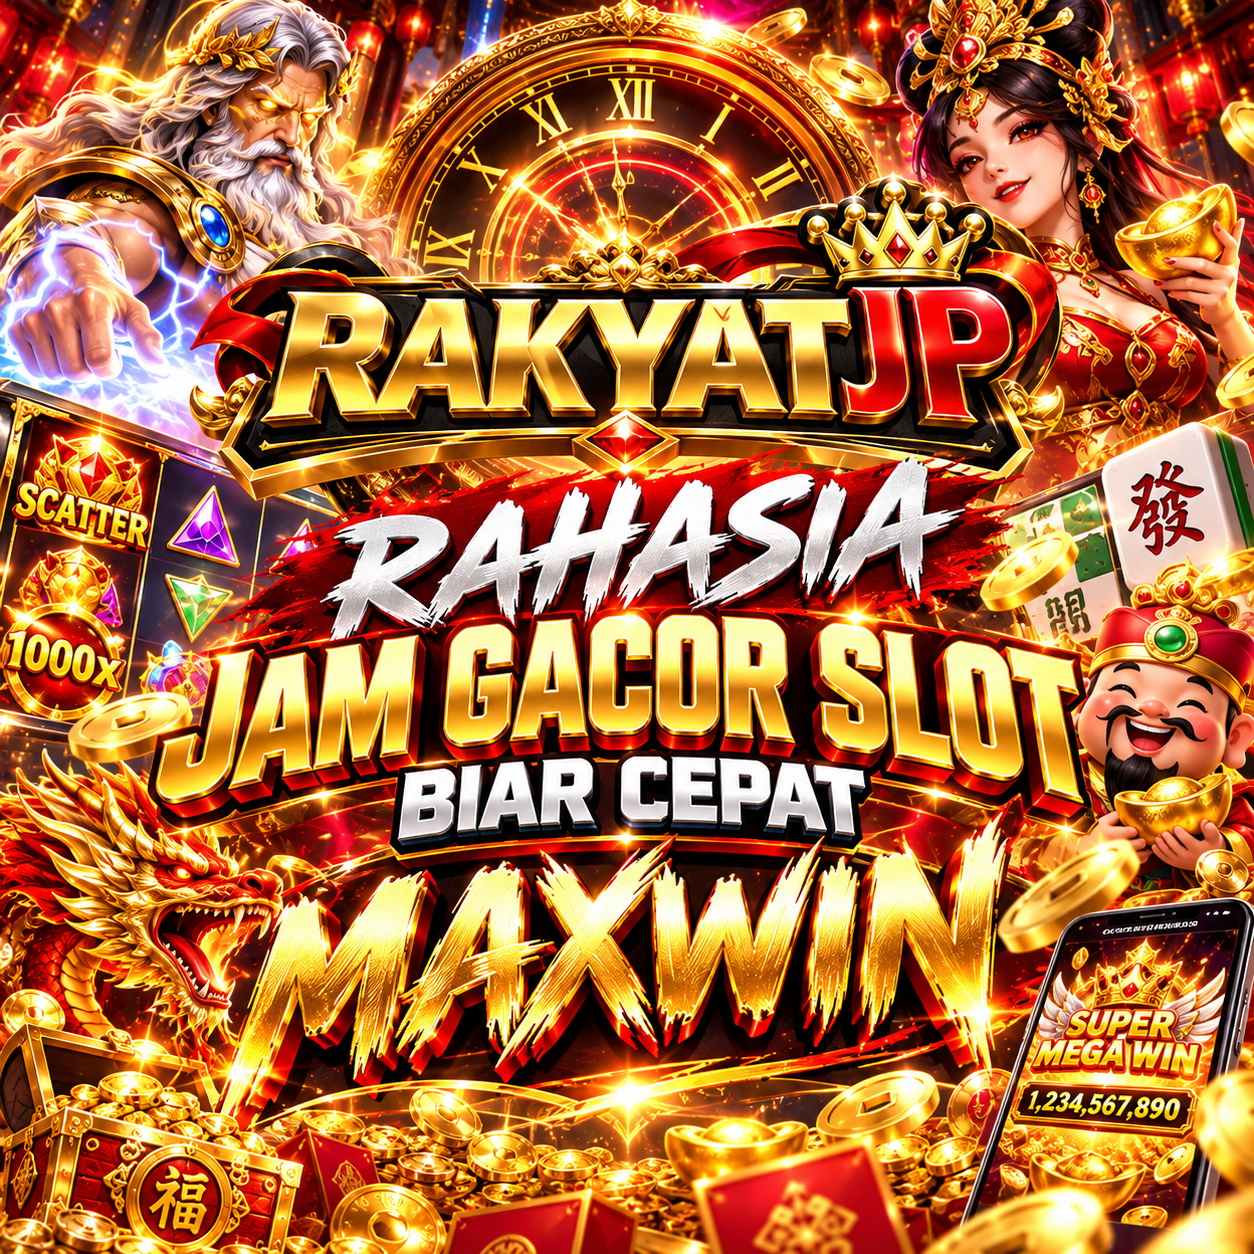
RAKYATJP: Rahasia Jam Gacor Slot Biar Cepat Maxwin

Detected technologies

(CMS)
Overall confidence: 100%
Detected patterns
  • /wp-(?:content|includes)/

(Analytics)
Overall confidence: 100%
Detected patterns
  • websdk\.appsflyer\.com

(Security)
Overall confidence: 100%
Detected patterns

(Analytics)
Overall confidence: 100%
Detected patterns
  • static\.cloudflareinsights\.com/beacon(?:\.min)?\.js

(Analytics)
Overall confidence: 100%
Detected patterns
  • script\.crazyegg\.com/pages/scripts/\d+/\d+\.js

(Advertising)
Overall confidence: 100%
Detected patterns
  • \.doubleclick\.net

(Analytics)
Overall confidence: 100%
Detected patterns
  • connect\.facebook.\w+/signals/config/\d+\?v=([\d\.]+)
  • connect\.facebook\.\w+/.+/fbevents\.js

(Analytics)
Overall confidence: 100%
Detected patterns
  • google-analytics\.com/(?:ga|urchin|analytics)\.js
  • googletagmanager\.com/gtag/js

(Tag managers)
Overall confidence: 100%
Detected patterns
  • \.googletagmanager\.com/
  • googletagmanager\.com/gtm\.js

(Affiliate programs)
Overall confidence: 100%
Detected patterns
  • utt\.impactcdn\.com

(Customer data platform)
Overall confidence: 100%
Detected patterns
  • api\.useinsider\.\w+/

(Customer data platform)
Overall confidence: 100%
Detected patterns
  • \.crwdcntrl\.net/

(Marketing automation)
Overall confidence: 100%
Detected patterns
  • cdn\.moengage\.\w+

(Advertising)
Overall confidence: 100%
Detected patterns
  • static\.ads-twitter\.com/uwt\.js

(Analytics)
Overall confidence: 100%
Detected patterns
  • analytics\.twitter\.com

(Analytics)
Overall confidence: 100%
Detected patterns
  • dev\.visualwebsiteoptimizer\.com/

Page Statistics

148
Requests

89 %
HTTPS

0 %
IPv6

34
Domains

39
Subdomains

38
IPs

6
Countries

5921 kB
Transfer

13847 kB
Size

24
Cookies

Redirected requests

There were HTTP redirect chains for the following requests:

Request Chain 75
  • https://googleads.g.doubleclick.net/pagead/viewthroughconversion/880395410/?random=1232230327&cv=11&fst=1726498673589&bg=ffffff&guid=ON&async=1&gtm=45be4990v877689920z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&label=hEx3CKjo-eADEJKJ56MD&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&value=0&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&capi=1&fmt=3&ct_cookie_present=false&crd=CLTesQII8t-xAgit4bECCK_hsQIIobixAgixwbECCLDBsQIIscOxAgiKxbECCMLJsQII1-ixAgi0xrECCIfbsQII08WxAgjrzLECCO3OsQII1c-xAgj02rECCOLqsQII6O6xAgiS67ECCMnjsQIIl9SxAgjJ27ECCM3msQIIpt2xAgiw3rECCIDbsQIIzeGxAgjL4bEC&cerd=ChCDsL4tueu-LZPuvi2d6bc4&eitems=ChEI8LiS1gYQ-Y_IobO6hrHxARIdAPOWweFfNDYQigTXYoDqSpe9X4S2fgRxZi23WjE&fsk=ChEI8LiS1gYQmNSM96yGof7IARIsACm40NJaAiKra6_dnSoP2qLNJ2J5R14ZFm1sfuVTK71_QDZBXmF1nNUBdAoaAusQ&pscrd=IhMI-NrM6Y-nlwMVyiZ7BB24TA1COiRodHRwczovL2RhZnRhcnNsb3R0ZXJwZXJjYXlhaWRuLmNvbS9CWENoRUk4TGlTMWdZUXM0djJ6YVdfdzl2UEFSSXRBQXVYbGhyYkUzeUZlN3dMNG8ySG9lSmE4d1Z2Snhra3FvWkV6STMxRkxrWDdYS3RyQ3FiU3V5MGRLeXZ6DAgJYggIABAAGAAgAA HTTP 302
  • https://www.google.com/pagead/1p-conversion/880395410/?random=1232230327&cv=11&fst=1726498673589&bg=ffffff&guid=ON&async=1&gtm=45be4990v877689920z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&label=hEx3CKjo-eADEJKJ56MD&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&value=0&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&capi=1&fmt=3&ct_cookie_present=false&crd=CLTesQII8t-xAgit4bECCK_hsQIIobixAgixwbECCLDBsQIIscOxAgiKxbECCMLJsQII1-ixAgi0xrECCIfbsQII08WxAgjrzLECCO3OsQII1c-xAgj02rECCOLqsQII6O6xAgiS67ECCMnjsQIIl9SxAgjJ27ECCM3msQIIpt2xAgiw3rECCIDbsQIIzeGxAgjL4bEC&cerd=ChCDsL4tueu-LZPuvi2d6bc4&fsk=ChEI8LiS1gYQmNSM96yGof7IARIsACm40NJaAiKra6_dnSoP2qLNJ2J5R14ZFm1sfuVTK71_QDZBXmF1nNUBdAoaAusQ&pscrd=IhMI-NrM6Y-nlwMVyiZ7BB24TA1COiRodHRwczovL2RhZnRhcnNsb3R0ZXJwZXJjYXlhaWRuLmNvbS9CWENoRUk4TGlTMWdZUXM0djJ6YVdfdzl2UEFSSXRBQXVYbGhyYkUzeUZlN3dMNG8ySG9lSmE4d1Z2Snhra3FvWkV6STMxRkxrWDdYS3RyQ3FiU3V5MGRLeXZ6DAgJYggIABAAGAAgAA&is_vtc=1&cid=CAQSXgBAziHcij5-FVbyy6156t-CWbN26tl0nU81PFVDh2QcEXv3mPmPYPHEmkqDXcbhAqRtHRVmOXWsuLx8OmEQTMbOmU7-9Dp8iyEGAuxSppXBuasNUVxyagfBXgqjJYo&eitems=ChEI8LiS1gYQ-Y_IobO6hrHxARIdAPOWweHHVOk-UMg9I8Km92jpbhxAfM5AOHxJZNg&random=574239686 HTTP 302
  • https://www.google.pl/pagead/1p-conversion/880395410/?random=1232230327&cv=11&fst=1726498673589&bg=ffffff&guid=ON&async=1&gtm=45be4990v877689920z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&label=hEx3CKjo-eADEJKJ56MD&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&value=0&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&capi=1&fmt=3&ct_cookie_present=false&crd=CLTesQII8t-xAgit4bECCK_hsQIIobixAgixwbECCLDBsQIIscOxAgiKxbECCMLJsQII1-ixAgi0xrECCIfbsQII08WxAgjrzLECCO3OsQII1c-xAgj02rECCOLqsQII6O6xAgiS67ECCMnjsQIIl9SxAgjJ27ECCM3msQIIpt2xAgiw3rECCIDbsQIIzeGxAgjL4bEC&cerd=ChCDsL4tueu-LZPuvi2d6bc4&fsk=ChEI8LiS1gYQmNSM96yGof7IARIsACm40NJaAiKra6_dnSoP2qLNJ2J5R14ZFm1sfuVTK71_QDZBXmF1nNUBdAoaAusQ&is_vtc=1&cid=CAQSXgBAziHcij5-FVbyy6156t-CWbN26tl0nU81PFVDh2QcEXv3mPmPYPHEmkqDXcbhAqRtHRVmOXWsuLx8OmEQTMbOmU7-9Dp8iyEGAuxSppXBuasNUVxyagfBXgqjJYo&eitems=ChEI8LiS1gYQ-Y_IobO6hrHxARIdAPOWweHHVOk-UMg9I8Km92jpbhxAfM5AOHxJZNg&random=574239686&ipr=y&pscrd=IhMI-NrM6Y-nlwMVyiZ7BB24TA1COiRodHRwczovL2RhZnRhcnNsb3R0ZXJwZXJjYXlhaWRuLmNvbS9CWENoRUk4TGlTMWdZUXM0djJ6YVdfdzl2UEFSSXRBQXVYbGhyYkUzeUZlN3dMNG8ySG9lSmE4d1Z2Snhra3FvWkV6STMxRkxrWDdYS3RyQ3FiU3V5MGRLeXZ6DAgJYggIABAAGAAgAA
Request Chain 96
  • https://asia.creativecdn.com/tags?id=pr_FAOiA95ZI30AXifJGDUt_offer_NUT-60023-01292-00001&id=pr_FAOiA95ZI30AXifJGDUt_uid_unknown HTTP 302
  • https://asia.creativecdn.com/tags?id=pr_FAOiA95ZI30AXifJGDUt_offer_NUT-60023-01292-00001&id=pr_FAOiA95ZI30AXifJGDUt_uid_unknown&tc=1
Request Chain 101
  • https://asia.creativecdn.com/tags?id=pr_FAOiA95ZI30AXifJGDUt_offer_NUT-60023-01292-00001&id=pr_FAOiA95ZI30AXifJGDUt_uid_unknown HTTP 302
  • https://asia.creativecdn.com/tags?id=pr_FAOiA95ZI30AXifJGDUt_offer_NUT-60023-01292-00001&id=pr_FAOiA95ZI30AXifJGDUt_uid_unknown&tc=1

148 HTTP transactions Go Pro

Only in urlscan Pro

Inspect WebSocket connections, examine POST data effortlessly, and track overlap counts in real time. Features live search and filtering across all HTTP output, complete with full response metadata for deep analysis.
Click for more information
Free trials of urlscan Pro are available.

0 data transactions

Method
Protocol
Status Resource
Path
Size
x-fer
Time
Latency
Type
MIME-Type
IP
Location
GET
H3
200
Primary Request / Show response
daftarslotterpercayaidn.com/
1 MB
97 KB
492ms
261ms
Document
text/html
172.67.155.237
Cloudflare
General
Full URL
https://daftarslotterpercayaidn.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.67.155.237 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
79bc978bffc509c0407154ae6e97676b93c84996cedbbc5a06cd4a34de052721

Request headers

Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

alt-svc
h3=":443"; ma=86400
cf-cache-status
DYNAMIC
cf-ray
a46a571d3e5e9d75-WAW
content-encoding
zstd
content-type
text/html
date
Wed, 07 Oct 2026 05:00:06 GMT
last-modified
Wed, 07 Oct 2026 04:58:12 GMT
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
priority
u=0,i
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=IKz83xPzyTWp98zvCVqoJ2E67zfQA6dINf0SCQC4bWIaZJhSyFLOWf391bOPK7cHDIGq2KWW%2BIwX7NBOiuiST%2FCxMzgiVf4i9wFKf3Lx6zxaOpYLCzKebAJQAtmfmflrsMCJTaQpPBteuC0WDXU%3D"}]}
server
cloudflare
server-timing
cfExtPri
vary
Accept-Encoding
GET
H3
200
/ Show response
websdk.appsflyer.com/
58 KB
17 KB
123ms
51ms
Script
application/javascript
18.64.211.102
Amazon.com
General
Full URL
https://websdk.appsflyer.com/?st=banners,pba&
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
18.64.211.102 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-18-64-211-102.fra56.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
7c008ff0e64ce1d8797d6afe11420b8d24ea4036f7ef1fc115575027e53ee132

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding, Origin
content-encoding
gzip
x-amz-version-id
sMMOBeKU10x6SB53mk.02XH2u9BPyawr
age
29
etag
W/"6a1891c62e62456c48bc6ab10d0403ab"
via
1.1 8d71893c94b38234ca2b7efa272a14b8.cloudfront.net (CloudFront)
alt-svc
h3=":443"; ma=86400
x-cache
Hit from cloudfront
x-amz-cf-id
Tf79ZQX0r9mLvUKznKydHipCAIvMRzW3x2vB5ywb6TBA_FKyOExnzA==
date
Wed, 07 Oct 2026 04:59:38 GMT
content-type
application/javascript
last-modified
Wed, 29 Jul 2026 12:19:08 GMT
server
AmazonS3
x-amz-cf-pop
FRA56-P16
x-amz-server-side-encryption
AES256
GET
H3
200
ca6be1649b2c6bd5aa79ebaa229fa676.js Show response
script.crazyegg.com/pages/versioned/trackingpagestate-scripts/
20 KB
8 KB
89ms
37ms
Script
text/javascript
104.19.147.8
Cloudflare
General
Full URL
https://script.crazyegg.com/pages/versioned/trackingpagestate-scripts/ca6be1649b2c6bd5aa79ebaa229fa676.js
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.19.147.8 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
7701282ea59743a1d336ee5ede4e6805ca9572c28ad013fa956fb39f18de0d69

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
cf-cache-status
HIT
age
116553
server-timing
cfExtPri
alt-svc
h3=":443"; ma=86400
date
Wed, 07 Oct 2026 05:00:06 GMT
content-type
text/javascript
last-modified
Wed, 25 Sep 2024 18:34:31 GMT
vary
accept-encoding
priority
u=3,i=?0
cache-control
public, max-age=31536000, s-maxage=31536000
timing-allow-origin
*
cf-ray
a46a571f3859bf47-WAW
accept-ranges
bytes
access-control-allow-origin
*
content-length
8032
server
cloudflare
GET
H3
200
db7349b994413162218df5c920535415.js Show response
script.crazyegg.com/pages/versioned/common-scripts/
103 KB
35 KB
42ms
35ms
Script
text/javascript
104.19.147.8
Cloudflare
General
Full URL
https://script.crazyegg.com/pages/versioned/common-scripts/db7349b994413162218df5c920535415.js
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.19.147.8 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
a4e043f37b5980394b4c7d6f3d55edecb9390249aa2f4de55a082a1bdfd27164

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
cf-cache-status
HIT
age
116554
server-timing
cfExtPri
alt-svc
h3=":443"; ma=86400
date
Wed, 07 Oct 2026 05:00:07 GMT
content-type
text/javascript
last-modified
Fri, 06 Sep 2024 19:46:55 GMT
vary
accept-encoding
priority
u=3,i=?0
cache-control
public, max-age=31536000, s-maxage=31536000
timing-allow-origin
*
cf-ray
a46a5724587dbf47-WAW
accept-ranges
bytes
access-control-allow-origin
*
content-length
35590
server
cloudflare
GET
H2
200
moe_webSdk.min.latest.js Show response
cdn.moengage.com/webpush/
401 KB
116 KB
63ms
56ms
Script
application/javascript
3.161.82.109
Amazon.com
General
Full URL
https://cdn.moengage.com/webpush/moe_webSdk.min.latest.js
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.109 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-109.fra56.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
c12c4ba7cfe24b418c778165afe99eb5193265d2403e440531d3f61887ff0a5c

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
cache-control
max-age=1209600
content-encoding
gzip
etag
W/"3220b140c4454fa8e687e75df9369aa2"
age
170534
via
1.1 0c32b42e3b5070fcbe6b5b320d0621b2.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
4JQfD-FgERGHOZ8wCBRn0esczcVjjFQzDrzz26qOpAkOSbE9FXuCrA==
date
Mon, 05 Oct 2026 05:37:54 GMT
content-type
application/javascript
last-modified
Mon, 05 Oct 2026 05:37:51 GMT
server
AmazonS3
x-amz-cf-pop
FRA56-P10
x-amz-server-side-encryption
AES256
GET
H2
200
ins.js Show response
blibli.api.useinsider.com/
0
481 B
332ms
58ms
Script
application/javascript
162.159.133.61
Cloudflare
General
Full URL
https://blibli.api.useinsider.com/ins.js?id=10001129
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
162.159.133.61 , United States, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 1

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cf-cache-status
HIT
x-amz-version-id
PxtiBxtLSjQmNUlRe.SB2GLWi5wUB_ti
etag
"d41d8cd98f00b204e9800998ecf8427e"
age
827
x-content-type-options
nosniff
expires
Wed, 07 Oct 2026 05:05:08 GMT
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Thu, 14 Mar 2024 08:46:20 GMT
vary
accept-encoding
x-frame-options
SAMEORIGIN
x-amz-id-2
Mz5gRCyJhhwCfTNitpAOQBc3dF+MiJGzt76Rt4uOa872BawdwNDPzrSvrr1IFZIjCw+V14Siedo=
strict-transport-security
max-age=31536000; includeSubDomains
cache-control
public, max-age=300
pragma
public
x-amz-request-id
62J24473CQ7F609E
cf-ray
a46a572608f5f59c-WAW
accept-ranges
bytes
access-control-allow-origin
*
content-length
0
x-xss-protection
1
server
cloudflare
GET
H2
200
A4103922-694c-4259-836a-1c467d2df1c71.js Show response
utt.impactcdn.com/
58 KB
24 KB
151ms
32ms
Script
text/javascript
35.186.249.72
Google LLC
General
Full URL
https://utt.impactcdn.com/A4103922-694c-4259-836a-1c467d2df1c71.js
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
35.186.249.72 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
72.249.186.35.bc.googleusercontent.com
Software
UploadServer /
Resource Hash
14791f324ed7deef8506110328b41d3f00c75fb5bf433a798a98ebbee36d3c53

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
content-encoding
gzip
x-goog-hash
crc32c=DQJBbQ==, md5=riKALMNPmRGcvoa0cJBykQ==
etag
"ae22802cc34f99119cbe86b470907291"
age
60
x-goog-stored-content-encoding
gzip
expires
Wed, 07 Oct 2026 05:04:07 GMT
alt-svc
h3=":443"; ma=2592000
x-goog-stored-content-length
24185
date
Wed, 07 Oct 2026 04:59:07 GMT
last-modified
Wed, 24 Jun 2026 15:01:55 GMT
content-type
text/javascript; charset=utf-8
vary
Accept-Encoding
x-guploader-uploadid
AP6rU81TcdGJSHJvDx03_I0TxlgAl2teNeRiyybnf_35EXHPL6iZ91MxIB0ucjRbVur09ZBIsb_djww
cache-control
public,max-age=900,s-maxage=300
x-goog-storage-class
MULTI_REGIONAL
accept-ranges
bytes
access-control-allow-origin
*
x-goog-generation
1782313315430472
content-length
24185
server
UploadServer
GET
H2
200
analytics.js Show response
www.google-analytics.com/
51 KB
21 KB
115ms
31ms
Script
text/javascript
216.239.32.178
Google LLC
General
Full URL
https://www.google-analytics.com/analytics.js
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
216.239.32.178 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
Golfe2 /
Resource Hash
f1a61277e3f902f50ab42015d8b07218db9b7601bb0967e54a52bfdcb4fa7e81
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
age
803
report-to
{"group":"ascnsrsgac:225:0","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/scaffolding/ascnsrsgac:225:0"}],}
x-content-type-options
nosniff
expires
Wed, 07 Oct 2026 06:46:44 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 07 Oct 2026 04:46:44 GMT
last-modified
Tue, 15 Jul 2025 00:44:26 GMT
content-type
text/javascript
vary
Accept-Encoding
strict-transport-security
max-age=31536000; includeSubDomains; preload
cache-control
public, max-age=7200
cross-origin-resource-policy
cross-origin
content-security-policy-report-only
script-src 'none'; form-action 'none'; frame-src 'none'; report-uri https://csp.withgoogle.com/csp/scaffolding/ascnsrsgac:225:0
cross-origin-opener-policy-report-only
same-origin; report-to=ascnsrsgac:225:0
content-length
20802
server
Golfe2
GET
H3
200
1060020737679640 Show response
connect.facebook.net/signals/config/
255 KB
83 KB
346ms
293ms
Script
application/x-javascript
57.144.244.128
Facebook
General
Full URL
https://connect.facebook.net/signals/config/1060020737679640?v=2.9.167&r=stable&domain=www.blibli.com&hme=da9a399065fb1c492026018b9e54864148adfb49d800f41752428fb7b59190f8&ex_m=69%2C118%2C104%2C108%2C60%2C4%2C97%2C68%2C16%2C94%2C86%2C50%2C53%2C168%2C171%2C183%2C179%2C180%2C182%2C29%2C98%2C52%2C75%2C181%2C163%2C166%2C176%2C177%2C184%2C127%2C40%2C34%2C139%2C15%2C49%2C190%2C189%2C129%2C18%2C39%2C1%2C42%2C64%2C65%2C66%2C70%2C90%2C17%2C14%2C93%2C89%2C88%2C105%2C51%2C107%2C38%2C106%2C30%2C91%2C26%2C164%2C167%2C136%2C28%2C11%2C12%2C13%2C6%2C7%2C25%2C22%2C23%2C56%2C61%2C63%2C73%2C99%2C27%2C74%2C9%2C8%2C78%2C47%2C21%2C101%2C100%2C102%2C95%2C10%2C20%2C3%2C19%2C83%2C55%2C81%2C33%2C72%2C0%2C92%2C32%2C80%2C85%2C46%2C45%2C84%2C37%2C5%2C87%2C79%2C43%2C35%2C82%2C2%2C36%2C62%2C41%2C103%2C44%2C77%2C67%2C109%2C59%2C58%2C31%2C96%2C57%2C54%2C48%2C76%2C71%2C24%2C110%2C196%2C195%2C197%2C202%2C203%2C204%2C200%2C192%2C128%2C159%2C191%2C193%2C119%2C153%2C141%2C147%2C185%2C186%2C125%2C228%2C113%2C124%2C229%2C161%2C116%2C231%2C162%2C132%2C120%2C150%2C144%2C111
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
57.144.244.128 Frankfurt am Main, Germany, ASN32934 (FACEBOOK - Facebook, Inc., US),
Reverse DNS
xx-fbcdn-shv-01-fra5.fbcdn.net
Software
/
Resource Hash
a137e0772b72a2f40d633cd0767f0f8b0d2fb8582a1d88b198d6a08e95a84e3a
Security Headers
Name Value
Content-Security-Policy default-src *.facebook.com *.fbcdn.net *.facebook.net 'self' blob:;script-src *.facebook.com *.fbcdn.net *.facebook.net blob: 'self' 'nonce-AeoI8KS4';style-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob: 'unsafe-inline';connect-src *.facebook.com facebook.com *.fbcdn.net *.facebook.net wss://*.facebook.com:* wss://*.fbcdn.net attachment.fbsbx.com *.cdninstagram.com blob: 'self' data: https://edge-chat.facebook.net https://edge-chat-latest.facebook.net wss://edge-chat-latest.facebook.net wss://edge-chat.facebook.net wss://edge-chat.socialplugin.facebook.net wss://edge-chat-latest.socialplugin.facebook.net https://edge-chat.socialplugin.facebook.net https://edge-chat-latest.socialplugin.facebook.net;font-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;img-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;media-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;child-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;frame-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;manifest-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;object-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;worker-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;block-all-mixed-content;upgrade-insecure-requests;report-uri https://www.facebook.com/csp/reporting/?m=c&minimize=0;
Strict-Transport-Security max-age=31536000; preload; includeSubDomains
X-Content-Type-Options nosniff
X-Frame-Options DENY
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
report-to
{"max_age":2592000,"endpoints":[{"url":"https:\/\/www.facebook.com\/browser_reporting\/coop\/?minimize=0"}],"group":"coop_report","include_subdomains":true}, {"max_age":86400,"endpoints":[{"url":"https:\/\/www.facebook.com\/browser_reporting\/coep\/?minimize=0"}],"group":"coep_report"}, {"max_age":21600,"endpoints":[{"url":"https:\/\/www.facebook.com\/ajax\/browser_error_reports\/"}],"group":"permissions_policy"}
x-content-type-options
nosniff
expires
Sat, 01 Jan 2000 00:00:00 GMT
alt-svc
h3=":443"; ma=86400
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
application/x-javascript; charset=utf-8
vary
Accept-Encoding
cross-origin-embedder-policy-report-only
require-corp;report-to="coep_report"
priority
u=3,i
x-frame-options
DENY
strict-transport-security
max-age=31536000; preload; includeSubDomains
reporting-endpoints
coop_report="https://www.facebook.com/browser_reporting/coop/?minimize=0", coep_report="https://www.facebook.com/browser_reporting/coep/?minimize=0", permissions_policy="https://www.facebook.com/ajax/browser_error_reports/"
content-security-policy
default-src *.facebook.com *.fbcdn.net *.facebook.net 'self' blob:;script-src *.facebook.com *.fbcdn.net *.facebook.net blob: 'self' 'nonce-AeoI8KS4';style-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob: 'unsafe-inline';connect-src *.facebook.com facebook.com *.fbcdn.net *.facebook.net wss://*.facebook.com:* wss://*.fbcdn.net attachment.fbsbx.com *.cdninstagram.com blob: 'self' data: https://edge-chat.facebook.net https://edge-chat-latest.facebook.net wss://edge-chat-latest.facebook.net wss://edge-chat.facebook.net wss://edge-chat.socialplugin.facebook.net wss://edge-chat-latest.socialplugin.facebook.net https://edge-chat.socialplugin.facebook.net https://edge-chat-latest.socialplugin.facebook.net;font-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;img-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;media-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;child-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;frame-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;manifest-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;object-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;worker-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;block-all-mixed-content;upgrade-insecure-requests;report-uri https://www.facebook.com/csp/reporting/?m=c&minimize=0;
cache-control
public, max-age=1200
timing-allow-origin
*
cross-origin-opener-policy
same-origin-allow-popups
x-fb-connection-quality
EXCELLENT; q=0.9, rtt=48, rtx=0, c=24, mss=1232, tbw=5037, tp=10, tpl=0, uplat=243, ullat=0
pragma
public
x-fb-debug
2Vrlcc8RIsl/Y0P41QVyDA/OBdEb9hJybmcfCgqyWdBJaE2UcnxZBThUGpB++uyJGhhq9IyJauoU+vCmpna/vw==
cross-origin-resource-policy
cross-origin
permissions-policy
accelerometer=(), attribution-reporting=(), autoplay=(), bluetooth=(), camera=(), ch-device-memory=(), ch-downlink=(), ch-dpr=(), ch-ect=(), ch-rtt=(), ch-save-data=(), ch-ua-arch=(), ch-ua-bitness=(), ch-viewport-height=(), ch-viewport-width=(), ch-width=(), clipboard-read=(), clipboard-write=(), compute-pressure=(), display-capture=(), encrypted-media=(), fullscreen=(self), gamepad=(), geolocation=(), gyroscope=(), hid=(), idle-detection=(), interest-cohort=(), keyboard-map=(), local-fonts=(), magnetometer=(), microphone=(), midi=(), otp-credentials=(), payment=(), picture-in-picture=(), private-state-token-issuance=(), publickey-credentials-get=(), screen-wake-lock=(), serial=(), shared-storage=(), shared-storage-select-url=(), private-state-token-redemption=(), usb=(), unload=(self), window-management=(), xr-spatial-tracking=();report-to="permissions_policy"
document-policy
force-load-at-top, include-js-call-stacks-in-crash-reports
x-xss-protection
0
origin-agent-cluster
?1
GET
H3
200
515463815273206 Show response
connect.facebook.net/signals/config/
65 KB
15 KB
531ms
477ms
Script
application/x-javascript
57.144.244.128
Facebook
General
Full URL
https://connect.facebook.net/signals/config/515463815273206?v=2.9.167&r=stable&domain=www.blibli.com&hme=da9a399065fb1c492026018b9e54864148adfb49d800f41752428fb7b59190f8&ex_m=69%2C118%2C104%2C108%2C60%2C4%2C97%2C68%2C16%2C94%2C86%2C50%2C53%2C168%2C171%2C183%2C179%2C180%2C182%2C29%2C98%2C52%2C75%2C181%2C163%2C166%2C176%2C177%2C184%2C127%2C40%2C34%2C139%2C15%2C49%2C190%2C189%2C129%2C18%2C39%2C1%2C42%2C64%2C65%2C66%2C70%2C90%2C17%2C14%2C93%2C89%2C88%2C105%2C51%2C107%2C38%2C106%2C30%2C91%2C26%2C164%2C167%2C136%2C28%2C11%2C12%2C13%2C6%2C7%2C25%2C22%2C23%2C56%2C61%2C63%2C73%2C99%2C27%2C74%2C9%2C8%2C78%2C47%2C21%2C101%2C100%2C102%2C95%2C10%2C20%2C3%2C19%2C83%2C55%2C81%2C33%2C72%2C0%2C92%2C32%2C80%2C85%2C46%2C45%2C84%2C37%2C5%2C87%2C79%2C43%2C35%2C82%2C2%2C36%2C62%2C41%2C103%2C44%2C77%2C67%2C109%2C59%2C58%2C31%2C96%2C57%2C54%2C48%2C76%2C71%2C24%2C110
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
57.144.244.128 Frankfurt am Main, Germany, ASN32934 (FACEBOOK - Facebook, Inc., US),
Reverse DNS
xx-fbcdn-shv-01-fra5.fbcdn.net
Software
/
Resource Hash
38cc5a6ce8c996a8b2885078031b76590e479c2dfc357f02909eb7b5c3433624
Security Headers
Name Value
Content-Security-Policy default-src *.facebook.com *.fbcdn.net *.facebook.net 'self' blob:;script-src *.facebook.com *.fbcdn.net *.facebook.net blob: 'self' 'nonce-LZXurLPy';style-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob: 'unsafe-inline';connect-src *.facebook.com facebook.com *.fbcdn.net *.facebook.net wss://*.facebook.com:* wss://*.fbcdn.net attachment.fbsbx.com *.cdninstagram.com blob: 'self' data: https://edge-chat.facebook.net https://edge-chat-latest.facebook.net wss://edge-chat-latest.facebook.net wss://edge-chat.facebook.net wss://edge-chat.socialplugin.facebook.net wss://edge-chat-latest.socialplugin.facebook.net https://edge-chat.socialplugin.facebook.net https://edge-chat-latest.socialplugin.facebook.net;font-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;img-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;media-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;child-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;frame-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;manifest-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;object-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;worker-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;block-all-mixed-content;upgrade-insecure-requests;report-uri https://www.facebook.com/csp/reporting/?m=c&minimize=0;
Strict-Transport-Security max-age=31536000; preload; includeSubDomains
X-Content-Type-Options nosniff
X-Frame-Options DENY
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
report-to
{"max_age":2592000,"endpoints":[{"url":"https:\/\/www.facebook.com\/browser_reporting\/coop\/?minimize=0"}],"group":"coop_report","include_subdomains":true}, {"max_age":86400,"endpoints":[{"url":"https:\/\/www.facebook.com\/browser_reporting\/coep\/?minimize=0"}],"group":"coep_report"}, {"max_age":21600,"endpoints":[{"url":"https:\/\/www.facebook.com\/ajax\/browser_error_reports\/"}],"group":"permissions_policy"}
x-content-type-options
nosniff
expires
Sat, 01 Jan 2000 00:00:00 GMT
alt-svc
h3=":443"; ma=86400
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
application/x-javascript; charset=utf-8
vary
Accept-Encoding
cross-origin-embedder-policy-report-only
require-corp;report-to="coep_report"
priority
u=3,i
x-frame-options
DENY
strict-transport-security
max-age=31536000; preload; includeSubDomains
reporting-endpoints
coop_report="https://www.facebook.com/browser_reporting/coop/?minimize=0", coep_report="https://www.facebook.com/browser_reporting/coep/?minimize=0", permissions_policy="https://www.facebook.com/ajax/browser_error_reports/"
content-security-policy
default-src *.facebook.com *.fbcdn.net *.facebook.net 'self' blob:;script-src *.facebook.com *.fbcdn.net *.facebook.net blob: 'self' 'nonce-LZXurLPy';style-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob: 'unsafe-inline';connect-src *.facebook.com facebook.com *.fbcdn.net *.facebook.net wss://*.facebook.com:* wss://*.fbcdn.net attachment.fbsbx.com *.cdninstagram.com blob: 'self' data: https://edge-chat.facebook.net https://edge-chat-latest.facebook.net wss://edge-chat-latest.facebook.net wss://edge-chat.facebook.net wss://edge-chat.socialplugin.facebook.net wss://edge-chat-latest.socialplugin.facebook.net https://edge-chat.socialplugin.facebook.net https://edge-chat-latest.socialplugin.facebook.net;font-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;img-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;media-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;child-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;frame-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;manifest-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;object-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;worker-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;block-all-mixed-content;upgrade-insecure-requests;report-uri https://www.facebook.com/csp/reporting/?m=c&minimize=0;
cache-control
public, max-age=1200
timing-allow-origin
*
cross-origin-opener-policy
same-origin-allow-popups
x-fb-connection-quality
EXCELLENT; q=0.9, rtt=48, rtx=0, c=89, mss=1232, tbw=95463, tp=88, tpl=0, uplat=427, ullat=0
pragma
public
x-fb-debug
m32zziOCUPxAMuVPfT7Mbs/Kp/BhQFd0OhJ7o2G0qRtwr0vbeyKrICUX32rXQytR9+FEI77DR7KWoUg+MlxgcA==
cross-origin-resource-policy
cross-origin
permissions-policy
accelerometer=(), attribution-reporting=(), autoplay=(), bluetooth=(), camera=(), ch-device-memory=(), ch-downlink=(), ch-dpr=(), ch-ect=(), ch-rtt=(), ch-save-data=(), ch-ua-arch=(), ch-ua-bitness=(), ch-viewport-height=(), ch-viewport-width=(), ch-width=(), clipboard-read=(), clipboard-write=(), compute-pressure=(), display-capture=(), encrypted-media=(), fullscreen=(self), gamepad=(), geolocation=(), gyroscope=(), hid=(), idle-detection=(), interest-cohort=(), keyboard-map=(), local-fonts=(), magnetometer=(), microphone=(), midi=(), otp-credentials=(), payment=(), picture-in-picture=(), private-state-token-issuance=(), publickey-credentials-get=(), screen-wake-lock=(), serial=(), shared-storage=(), shared-storage-select-url=(), private-state-token-redemption=(), usb=(), unload=(self), window-management=(), xr-spatial-tracking=();report-to="permissions_policy"
document-policy
force-load-at-top, include-js-call-stacks-in-crash-reports
x-xss-protection
0
origin-agent-cluster
?1
GET
H2
200
index.5da5dd52.css
www.static-src.com/frontend/static/
392 KB
40 KB
542ms
364ms
Stylesheet
text/css
34.117.1.79
Google LLC
General
Full URL
https://www.static-src.com/frontend/static/index.5da5dd52.css
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.117.1.79 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
79.1.117.34.bc.googleusercontent.com
Software
openresty /
Resource Hash
dbfaa41c979bbb839f78a4470b0a0e119262c06390e95d48e13ffd5c994ce1f1

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
content-encoding
gzip
x-goog-hash
crc32c=wG3bsA==, md5=j04f6CD2/lc4TOu99APtvA==
etag
"8f4e1fe820f6fe57384cebbdf403edbc"
x-goog-stored-content-encoding
gzip
expires
Thu, 07 Oct 2027 05:00:07 GMT
alt-svc
h3=":443"; ma=2592000
x-goog-stored-content-length
40604
date
Wed, 07 Oct 2026 05:00:07 GMT
content-type
text/css
vary
Origin
last-modified
Wed, 04 Sep 2024 15:11:57 GMT
x-guploader-uploadid
AP6rU82PyWWPlNeFnUBnMVHFPH6IkX_QrUTrQInilqez45KWL6n5520dRtDl2jSpO0SWe82K
x-cache-status
HIT
cache-control
max-age=31536000, public
x-goog-storage-class
REGIONAL
via
1.1 google
accept-ranges
bytes
access-control-allow-origin
https://www.blibli.com
x-goog-generation
1725462717964444
content-length
40604
server
openresty
GET

thematic_configuration_non_canary.js
www.blibli.com/backend/content/thematic/
0
0


GET

CustomerLocation.49933ea8.js
www.static-src.com/frontend/static/js/
0
0


GET

address-event.0a54fb2b.js
www.static-src.com/frontend/static/js/
0
0


GET

Location.c79a4a93.js
www.static-src.com/frontend/static/js/
0
0


GET

customer-location-mixin.dd72e66a.js
www.static-src.com/frontend/static/js/
0
0


GET
H2
200
CustomerLocation.d45a5c3d.css
www.static-src.com/frontend/static/
3 KB
1 KB
541ms
364ms
Stylesheet
text/css
34.117.1.79
Google LLC
General
Full URL
https://www.static-src.com/frontend/static/CustomerLocation.d45a5c3d.css
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.117.1.79 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
79.1.117.34.bc.googleusercontent.com
Software
openresty /
Resource Hash
d45a5c3d6cfa97ac248077fdfdece56c05f88e3b02ba06175cd2696cfaa6f653

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
content-encoding
gzip
x-goog-hash
crc32c=x0d8sw==, md5=Kyqu6JEr/9pas902xKSNAA==
etag
"2b2aaee8912bffda5ab3dd36c4a48d00"
x-goog-stored-content-encoding
gzip
expires
Thu, 07 Oct 2027 05:00:07 GMT
alt-svc
h3=":443"; ma=2592000
x-goog-stored-content-length
825
date
Wed, 07 Oct 2026 05:00:07 GMT
content-type
text/css
vary
Origin
last-modified
Tue, 29 Apr 2025 15:11:59 GMT
x-guploader-uploadid
AP6rU83iAKukMm66TcYLobXpD3awt_myZiAmn9PwoPWm7wrAsHJX0DxEDsoOFIMKcc_qPZHI
x-cache-status
HIT
cache-control
max-age=31536000, public
x-goog-storage-class
REGIONAL
via
1.1 google
accept-ranges
bytes
access-control-allow-origin
https://www.blibli.com
x-goog-generation
1745939519116567
content-length
825
server
openresty
GET
H2
200
moe_webSdk_webp.min.latest.js Show response
cdn.moengage.com/release/dc_1/
147 KB
47 KB
256ms
100ms
Script
application/javascript
3.161.82.109
Amazon.com
General
Full URL
https://cdn.moengage.com/release/dc_1/moe_webSdk_webp.min.latest.js?app_id=QTD7QXC51X5DZR3CTIHK33PQ
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.109 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-109.fra56.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
10f3cb8013466a17604698d4c6d662f8ba065d3bab865b519d79490ba0e91b5b

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
cache-control
max-age=1209600
content-encoding
gzip
etag
W/"69cb8337c3313473b9235caeae18462e"
age
170511
via
1.1 0c32b42e3b5070fcbe6b5b320d0621b2.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
TRGYNY1Xr5dfyUWnLOhAu7NrYnA8XtVLkpsg2hxId1E1F6-fWePqxQ==
date
Mon, 05 Oct 2026 05:38:17 GMT
content-type
application/javascript
last-modified
Mon, 05 Oct 2026 05:38:14 GMT
server
AmazonS3
x-amz-cf-pop
FRA56-P10
x-amz-server-side-encryption
AES256
GET

index.js
www.blibli.com/bwa/2.4.5-0/
0
0


GET
H2
200
j.php Show response
dev.visualwebsiteoptimizer.com/
110 B
307 B
563ms
58ms
Script
application/javascript
34.107.218.251
Google LLC
General
Full URL
https://dev.visualwebsiteoptimizer.com/j.php?a=426670&u=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FmetaData%3D4eHyfurj4yL7Q4Ucv84uGYHJb0g2t%2BFdwECMb3QsHNjtAqmaWkaBfGgt5w9qTEikAP03CsR8aLRQodyhRwzA9w%3D%3D%26pickupPointCode%3DPP-3495802&f=1&vn=1.5
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.107.218.251 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
251.218.107.34.bc.googleusercontent.com
Software
gams2 /
Resource Hash
543a2bc3bdebec6bc98871c2f227d07e725618df26154df87e5504b1d73f2c63
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains; preload
timing-allow-origin
*
content-encoding
gzip
via
1.1 google
access-control-allow-origin
*
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 07 Oct 2026 05:00:07 GMT
content-type
application/javascript; charset=UTF-8
server
gams2
GET
H3
200
/ Show response
googleads.g.doubleclick.net/pagead/viewthroughconversion/880395410/
8 KB
3 KB
155ms
95ms
Script
text/javascript
142.251.13.154
Google LLC
General
Full URL
https://googleads.g.doubleclick.net/pagead/viewthroughconversion/880395410/?random=1726498671571&cv=11&fst=1726498671571&bg=ffffff&guid=ON&async=1&gtm=45je4990v877689920z8810058345za200zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FmetaData%3D4eHyfurj4yL7Q4Ucv84uGYHJb0g2t%2BFdwECMb3QsHNjtAqmaWkaBfGgt5w9qTEikAP03CsR8aLRQodyhRwzA9w%3D%3D%26pickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Online%20Mall%20Blibli.com%2C%20Sensasi%20Belanja%20Online%20Shop%20ala%20Mall&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=event%3Dgtag.config&rfmt=3&fmt=4
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.13.154 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
wt-in-f154.1e100.net
Software
cafe /
Resource Hash
9d6b9d47e1ec88f46c7a91dc602a947e3500e0cfc3c4df0d9faeb24d2dde3925
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, must-revalidate
timing-allow-origin
*
content-encoding
br
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
content-length
3042
date
Wed, 07 Oct 2026 05:00:07 GMT
x-xss-protection
0
content-type
text/javascript; charset=UTF-8
content-disposition
attachment; filename="f.txt"
server
cafe
GET
H2
200
va-42b830ab1f45f2a5aa737b55d5e9e251.js Show response
dev.visualwebsiteoptimizer.com/7.0/
260 KB
73 KB
555ms
51ms
Script
text/javascript
34.107.218.251
Google LLC
General
Full URL
https://dev.visualwebsiteoptimizer.com/7.0/va-42b830ab1f45f2a5aa737b55d5e9e251.js
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.107.218.251 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
251.218.107.34.bc.googleusercontent.com
Software
gams2 /
Resource Hash
8bdc0627259cf14bdcf48d3351710ab6c23ad23289427e977a1d9df48ee62793
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload

Request headers

Origin
https://daftarslotterpercayaidn.com
sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains; preload
cache-control
public,max-age=31536000
timing-allow-origin
*
content-encoding
br
etag
"6ac5cd23-1237e"
via
1.1 google
accept-ranges
bytes
access-control-allow-origin
*
alt-svc
h3=":443"; ma=2592000
content-length
74622
date
Wed, 07 Oct 2026 05:00:07 GMT
content-type
text/javascript; charset=UTF-8
last-modified
Wed, 07 Oct 2026 04:40:03 GMT
server
gams2
vary
Accept-Encoding
GET
H2
200
track-42b830ab1f45f2a5aa737b55d5e9e251.js Show response
dev.visualwebsiteoptimizer.com/7.0/
19 KB
6 KB
634ms
129ms
Script
text/javascript
34.107.218.251
Google LLC
General
Full URL
https://dev.visualwebsiteoptimizer.com/7.0/track-42b830ab1f45f2a5aa737b55d5e9e251.js
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.107.218.251 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
251.218.107.34.bc.googleusercontent.com
Software
gams2 /
Resource Hash
80e1acedc648d6d06f06342e0db58dbd7f965c569da8f80aa3f0bfb29247e6d2
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload

Request headers

Origin
https://daftarslotterpercayaidn.com
sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains; preload
cache-control
public,max-age=31536000
timing-allow-origin
*
content-encoding
br
etag
"6ac5cd23-15fd"
via
1.1 google
accept-ranges
bytes
access-control-allow-origin
*
alt-svc
h3=":443"; ma=2592000
content-length
5629
date
Wed, 07 Oct 2026 05:00:07 GMT
content-type
text/javascript; charset=UTF-8
last-modified
Wed, 07 Oct 2026 04:40:03 GMT
server
gams2
vary
Accept-Encoding
GET
H2
200
opa-d2a84d50a8e7e2cafb7a1d7eb2fa92ef.js Show response
dev.visualwebsiteoptimizer.com/analysis/4.0/
234 KB
57 KB
627ms
123ms
Script
application/javascript
34.107.218.251
Google LLC
General
Full URL
https://dev.visualwebsiteoptimizer.com/analysis/4.0/opa-d2a84d50a8e7e2cafb7a1d7eb2fa92ef.js
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.107.218.251 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
251.218.107.34.bc.googleusercontent.com
Software
gams2 /
Resource Hash
3433dacfefe0557bcee1f621a276ecfea38a3fc6f5005c06d8186f28000d15d7
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload

Request headers

Origin
https://daftarslotterpercayaidn.com
sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains; preload
cache-control
public,max-age=31536000
timing-allow-origin
*
content-encoding
br
etag
"6ac5cd1b-e452"
via
1.1 google
accept-ranges
bytes
access-control-allow-origin
*
alt-svc
h3=":443"; ma=2592000
content-length
58450
date
Wed, 07 Oct 2026 05:00:07 GMT
content-type
application/javascript; charset=UTF-8
last-modified
Wed, 07 Oct 2026 04:39:55 GMT
server
gams2
vary
Accept-Encoding
GET
H3
200
/ Show response
googleads.g.doubleclick.net/pagead/viewthroughconversion/925089264/
8 KB
3 KB
139ms
80ms
Script
text/javascript
142.251.13.154
Google LLC
General
Full URL
https://googleads.g.doubleclick.net/pagead/viewthroughconversion/925089264/?random=1726498673524&cv=11&fst=1726498673524&bg=ffffff&guid=ON&async=1&gtm=45be4990z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=ecomm_pagetype%3Dproduct%3Becomm_prodid%3DNUT-60023-01292%3Becomm_totalvalue%3D343900&rfmt=3&fmt=4
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.13.154 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
wt-in-f154.1e100.net
Software
cafe /
Resource Hash
ba0b7eb3715835052d209004edb5678fb16783f5cbb27214e581570c4124ff92
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, must-revalidate
timing-allow-origin
*
content-encoding
br
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
content-length
3062
date
Wed, 07 Oct 2026 05:00:07 GMT
x-xss-protection
0
content-type
text/javascript; charset=UTF-8
content-disposition
attachment; filename="f.txt"
server
cafe
GET
H3
200
/ Show response
googleads.g.doubleclick.net/pagead/viewthroughconversion/920334631/
8 KB
3 KB
166ms
107ms
Script
text/javascript
142.251.13.154
Google LLC
General
Full URL
https://googleads.g.doubleclick.net/pagead/viewthroughconversion/920334631/?random=1726498673536&cv=11&fst=1726498673536&bg=ffffff&guid=ON&async=1&gtm=45be4990z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=ecomm_pagetype%3Dretail-product-detail%3Becomm_prodid%3DNUT-60023-01292%3Becomm_totalvalue%3D343900&rfmt=3&fmt=4
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.13.154 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
wt-in-f154.1e100.net
Software
cafe /
Resource Hash
cce72e79b42c4436f8bae6d1ec8c6e8b08049a7cab38863cba3bb29925f44785
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, must-revalidate
timing-allow-origin
*
content-encoding
br
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
content-length
3065
date
Wed, 07 Oct 2026 05:00:07 GMT
x-xss-protection
0
content-type
text/javascript; charset=UTF-8
content-disposition
attachment; filename="f.txt"
server
cafe
GET
H3
200
/ Show response
www.googleadservices.com/pagead/conversion/880395410/
9 KB
3 KB
126ms
64ms
Script
text/javascript
142.251.13.154
Google LLC
General
Full URL
https://www.googleadservices.com/pagead/conversion/880395410/?random=1726498673589&cv=11&fst=1726498673589&bg=ffffff&guid=ON&async=1&gtm=45be4990v877689920z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&label=hEx3CKjo-eADEJKJ56MD&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&value=0&bttype=purchase&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&capi=1&rfmt=3&fmt=4
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.13.154 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
wt-in-f154.1e100.net
Software
cafe /
Resource Hash
cad998d3504e0f3dd554c65cc4362db2db12b0a46d4aee2b9a9eee75720a9d30
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, must-revalidate
timing-allow-origin
*
content-encoding
br
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
3433
date
Wed, 07 Oct 2026 05:00:07 GMT
x-xss-protection
0
content-type
text/javascript; charset=UTF-8
content-disposition
attachment; filename="f.txt"
server
cafe
GET

FootSection.709acb56.js
www.static-src.com/frontend/static/js/
0
0


GET

AccordionContent.6cf8e4dd.js
www.static-src.com/frontend/static/js/
0
0


GET
H2
200
FootSection.a31a2cbc.css
www.static-src.com/frontend/static/
6 KB
1 KB
530ms
358ms
Stylesheet
text/css
34.117.1.79
Google LLC
General
Full URL
https://www.static-src.com/frontend/static/FootSection.a31a2cbc.css
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.117.1.79 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
79.1.117.34.bc.googleusercontent.com
Software
openresty /
Resource Hash
a31a2cbca80845eb52a64aac7d169d1ed00b9d9770598d565f410ecf2f0fbe4f

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
content-encoding
gzip
x-goog-hash
crc32c=YLzJ2Q==, md5=0Hi2LmeRd+CDkKLv6mCX2g==
etag
"d078b62e679177e08390a2efea6097da"
x-goog-stored-content-encoding
gzip
expires
Thu, 07 Oct 2027 05:00:07 GMT
alt-svc
h3=":443"; ma=2592000
x-goog-stored-content-length
1218
date
Wed, 07 Oct 2026 05:00:07 GMT
content-type
text/css
vary
Origin
last-modified
Thu, 03 Jul 2025 15:29:49 GMT
x-guploader-uploadid
AP6rU80XE9PFjZERHUafdF6cbe4u55q0Xwb2kWcqcJ8aYuO7Xu9GSbu9vhxOI4zbyHLgaQCYfjZ5YsM
x-cache-status
HIT
cache-control
max-age=31536000, public
x-goog-storage-class
REGIONAL
via
1.1 google
accept-ranges
bytes
access-control-allow-origin
https://www.blibli.com
x-goog-generation
1751556589856051
content-length
1218
server
openresty
GET

FooterDetail.22d2666a.js
www.static-src.com/frontend/static/js/
0
0


GET

index.5457813a.js
www.static-src.com/frontend/static/js/
0
0


GET

LazyImage.92de27af.js
www.static-src.com/frontend/static/js/
0
0


GET
H2
200
LazyImage.7ad1d4cb.css
www.static-src.com/frontend/static/
5 KB
1 KB
533ms
363ms
Stylesheet
text/css
34.117.1.79
Google LLC
General
Full URL
https://www.static-src.com/frontend/static/LazyImage.7ad1d4cb.css
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.117.1.79 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
79.1.117.34.bc.googleusercontent.com
Software
openresty /
Resource Hash
7ad1d4cb7d63f41b6ccd3444a64a5b753e777aa0aa101df63875fe59362d423c

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
content-encoding
gzip
x-goog-hash
crc32c=TnvWXA==, md5=YIqzxLivEDFw7BFxq1+Flg==
etag
"608ab3c4b8af103170ec1171ab5f8596"
x-goog-stored-content-encoding
gzip
expires
Thu, 07 Oct 2027 05:00:07 GMT
alt-svc
h3=":443"; ma=2592000
x-goog-stored-content-length
886
date
Wed, 07 Oct 2026 05:00:07 GMT
content-type
text/css
vary
Origin
last-modified
Thu, 03 Jul 2025 15:29:50 GMT
x-guploader-uploadid
AP6rU83Aljxj7g_H_JdYZa2wXwph1nhcoRiS6BKLHEvNc5pbYfUJCJ8JJtH602AOWfBMSLU38nZWZ7I
x-cache-status
HIT
cache-control
max-age=31536000, public
x-goog-storage-class
REGIONAL
via
1.1 google
accept-ranges
bytes
access-control-allow-origin
https://www.blibli.com
x-goog-generation
1751556590307411
content-length
886
server
openresty
GET

BlibliRouter.a4a077a8.js
www.static-src.com/frontend/static/js/
0
0


GET
H2
200
FooterDetail.783b18e8.css
www.static-src.com/frontend/static/
8 KB
2 KB
528ms
358ms
Stylesheet
text/css
34.117.1.79
Google LLC
General
Full URL
https://www.static-src.com/frontend/static/FooterDetail.783b18e8.css
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.117.1.79 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
79.1.117.34.bc.googleusercontent.com
Software
openresty /
Resource Hash
783b18e86fc50a89ad8b683a1a7f61ee77da33e169b0c674d11f712c1d863917

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
content-encoding
gzip
x-goog-hash
crc32c=jkhYEQ==, md5=0ODrqPd5E9y1gKQy41KWkA==
etag
"d0e0eba8f77913dcb580a432e3529690"
x-goog-stored-content-encoding
gzip
expires
Thu, 07 Oct 2027 05:00:07 GMT
alt-svc
h3=":443"; ma=2592000
x-goog-stored-content-length
1425
date
Wed, 07 Oct 2026 05:00:07 GMT
content-type
text/css
vary
Origin
last-modified
Thu, 03 Oct 2024 14:50:16 GMT
x-guploader-uploadid
AP6rU83h4LH7o2NOp6n94YvpvJY5UuZwAmMNEladdtfo_ff4Tb3R6hYwL1CsYjUC9mBKaoH7
x-cache-status
HIT
cache-control
max-age=31536000, public
x-goog-storage-class
REGIONAL
via
1.1 google
accept-ranges
bytes
access-control-allow-origin
https://www.blibli.com
x-goog-generation
1727967016409081
content-length
1425
server
openresty
GET
H2
200
/ Show response
prod.flixgvid.flix360.io/
59 B
360 B
765ms
623ms
Script
application/json
108.138.26.69
Amazon.com
General
Full URL
https://prod.flixgvid.flix360.io/
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
108.138.26.69 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-108-138-26-69.fra56.r.cloudfront.net
Software
CloudFront /
Resource Hash
cb42c57757d45d43019fde11ca7964ff5ce63026c2e3d25f29586a7bba20e1d7

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=157680000000
via
1.1 d34cf2ddbdf9774517330fee6a26e4b2.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Miss from cloudfront
content-length
59
x-amz-cf-id
rQtXRMGPc4kPXdiXKYx8bLSMGT1mrTcuGKp0G17A130Rye_gIvhTDQ==
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
application/json;charset=utf-8
x-amz-cf-pop
FRA56-P7
server
CloudFront
GET
H2
200
/ Show response
media.flixcar.com/modular/js/minify/12612/
2 KB
1 KB
265ms
122ms
Script
text/javascript
18.64.211.128
Amazon.com
General
Full URL
https://media.flixcar.com/modular/js/minify/12612/?url=static/distributor/12612/pagedata-specific.js
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
18.64.211.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-18-64-211-128.fra56.r.cloudfront.net
Software
CloudFront /
Resource Hash
10114649a2879814546a925ec8e98c011fae099aa68d45f864ba9c07467da14e

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
64
x-amzn-requestid
79386a4b-e640-47db-99d5-4acc1780fa66
x-cache
Hit from cloudfront
x-amz-cf-id
X9ye_SS1vePQNyUudDIOs2Jw3M4vEgNCfvMUdNpV9FA4sH4L5BuRPQ==
date
Wed, 07 Oct 2026 04:59:03 GMT
content-type
text/javascript;charset=UTF-8
vary
Accept-Encoding, Origin
cache-control
public, max-age=2000000, s-maxage=2000000, immutable
timing-allow-origin
*
x-amz-apigw-id
E22vsGYLLPEEhrQ=
x-amzn-trace-id
Root=1-6ac5d197-0f0cccde5eb1ae280258fdd2;Parent=138a2be5b81ad30b;Sampled=0;Lineage=1:16d39d59:0
via
1.1 5a72017819a4d0e7396f988900864d68.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-amz-cf-pop
FRA56-P16
server
CloudFront
GET
H2
200
/ Show response
media.flixcar.com/modular/js/minify/12612/
291 KB
38 KB
246ms
103ms
Script
text/javascript
18.64.211.128
Amazon.com
General
Full URL
https://media.flixcar.com/modular/js/minify/12612/?url=/static/tracking/tracking.js
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
18.64.211.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-18-64-211-128.fra56.r.cloudfront.net
Software
CloudFront /
Resource Hash
8e29c2c9cca933ffa27caf938488369160297167cf9486ec955bb99bc1cd1182

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
63
x-amzn-requestid
79424bb2-0a08-479a-b4c1-738457ac695b
x-cache
Hit from cloudfront
x-amz-cf-id
3o8330-5vBQni_2rPXdQn0hLBclxOtjHbx4KgNvcxVeDRJS80MLAZg==
date
Wed, 07 Oct 2026 04:59:04 GMT
content-type
text/javascript;charset=UTF-8
vary
Accept-Encoding, Origin
cache-control
public, max-age=2000000, s-maxage=2000000, immutable
timing-allow-origin
*
x-amz-apigw-id
E22vsEz-rPEEuVw=
x-amzn-trace-id
Root=1-6ac5d197-7d05a63c039d435e259bf12a;Parent=186a0dde2d6fdd39;Sampled=0;Lineage=1:16d39d59:0
via
1.1 5a72017819a4d0e7396f988900864d68.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-amz-cf-pop
FRA56-P16
server
CloudFront
GET
H3
200
/ Show response
googleads.g.doubleclick.net/pagead/viewthroughconversion/925089264/
8 KB
3 KB
75ms
74ms
Script
text/javascript
142.251.13.154
Google LLC
General
Full URL
https://googleads.g.doubleclick.net/pagead/viewthroughconversion/925089264/?random=1726498714047&cv=11&fst=1726498714047&bg=ffffff&guid=ON&async=1&gtm=45be4990z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1024&u_h=824&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=ecomm_pagetype%3Dproduct%3Becomm_prodid%3DNUT-60023-01292%3Becomm_totalvalue%3D343900&rfmt=3&fmt=4
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.13.154 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
wt-in-f154.1e100.net
Software
cafe /
Resource Hash
5754889f70f64e2822a0630a8416d0292e00014297d8d585fdcb39bd8e977a03
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, must-revalidate
timing-allow-origin
*
content-encoding
br
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
content-length
3073
date
Wed, 07 Oct 2026 05:00:07 GMT
x-xss-protection
0
content-type
text/javascript; charset=UTF-8
content-disposition
attachment; filename="f.txt"
server
cafe
GET
H3
200
/ Show response
googleads.g.doubleclick.net/pagead/viewthroughconversion/920334631/
8 KB
3 KB
92ms
92ms
Script
text/javascript
142.251.13.154
Google LLC
General
Full URL
https://googleads.g.doubleclick.net/pagead/viewthroughconversion/920334631/?random=1726498714059&cv=11&fst=1726498714059&bg=ffffff&guid=ON&async=1&gtm=45be4990z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1024&u_h=824&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=ecomm_pagetype%3Dretail-product-detail%3Becomm_prodid%3DNUT-60023-01292%3Becomm_totalvalue%3D343900&rfmt=3&fmt=4
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.13.154 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
wt-in-f154.1e100.net
Software
cafe /
Resource Hash
cf44b1cf8d9d8d9f553d8d66bacd621fbedf51aa2c933360e26ff12aa2673457
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, must-revalidate
timing-allow-origin
*
content-encoding
br
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://googleads.g.doubleclick.net/pagead/gcn_p3p_.xml", CP="CURa ADMa DEVa TAIo PSAo PSDo OUR IND UNI PUR INT DEM STA PRE COM NAV OTC NOI DSP COR"
content-length
3079
date
Wed, 07 Oct 2026 05:00:07 GMT
x-xss-protection
0
content-type
text/javascript; charset=UTF-8
content-disposition
attachment; filename="f.txt"
server
cafe
GET
H2
200
js Show response
www.googletagmanager.com/gtag/
522 KB
175 KB
212ms
80ms
Script
application/javascript
192.178.183.97
Google LLC
General
Full URL
https://www.googletagmanager.com/gtag/js?id=G-SF0EQEXKPW
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
192.178.183.97 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfraw-in-f97.1e100.net
Software
Google Tag Manager /
Resource Hash
e2c6fdea2cb55187591f6713804205d250f8f36cec70bdfb74b247f0181936f5
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains
cache-control
private, max-age=900
content-encoding
zstd
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
expires
Wed, 07 Oct 2026 05:00:08 GMT
access-control-allow-origin
*
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
178503
date
Wed, 07 Oct 2026 05:00:08 GMT
x-xss-protection
0
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
server
Google Tag Manager
access-control-allow-headers
Cache-Control
GET
H3
200
logorakyatjp.webp
meubelkayumurah.pics/wp-content/uploads/2026/05/
20 KB
21 KB
115ms
37ms
Image
image/webp
188.114.97.3
Cloudflare
General
Full URL
https://meubelkayumurah.pics/wp-content/uploads/2026/05/logorakyatjp.webp
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
188.114.97.3 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
5c4ff6f1f404bf857f698d88077aa607d3c1efb125748e69932584aa0596704a

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=14400
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
cf-cache-status
HIT
age
4389
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=R2LfWIiVMzS0w4bj2O%2BmKANNapZrBYbbRyLFdawq2%2FTTOdMsJQnTGY9ksQQAxir3FNym3DUzb8t1t1CZRDObsJKPgf1ml4g4wgHe1RsNCeIQTtx8cyc5x4idhSbLWDontwztwTgPlA%3D%3D"}]}
cf-ray
a46a571fba23cf5c-WAW
accept-ranges
bytes
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
content-length
20766
date
Wed, 07 Oct 2026 05:00:06 GMT
content-type
image/webp
last-modified
Mon, 18 May 2026 11:14:53 GMT
server
cloudflare
priority
u=3,i
GET
H2
200
no_brand_mystery_box_full01_b7kg1a4y.jpg
www.static-src.com/wcsstore/Indraprastha/images/catalog/medium/catalog-image/105/MTA-178175238/
8 KB
9 KB
362ms
362ms
Image
image/webp
34.117.1.79
Google LLC
General
Full URL
https://www.static-src.com/wcsstore/Indraprastha/images/catalog/medium/catalog-image/105/MTA-178175238/no_brand_mystery_box_full01_b7kg1a4y.jpg
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.117.1.79 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
79.1.117.34.bc.googleusercontent.com
Software
openresty /
Resource Hash
c5007d87986fb629a4bc65de165f596febfbe3c2f0e65a88f5a75a1092b4e7e7

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
x-robots-tag
index
x-goog-hash
crc32c=to1BzQ==, md5=gb47EuAqw79r8ppVuT0nkQ==
etag
"81be3b12e02ac3bf6bf29a55b93d2791"
x-goog-stored-content-encoding
identity
x-width-folder
original
expires
Thu, 07 Oct 2027 05:00:07 GMT
alt-svc
h3=":443"; ma=2592000
x-goog-stored-content-length
8558
date
Wed, 07 Oct 2026 05:00:07 GMT
content-type
image/webp
last-modified
Fri, 25 Sep 2026 08:18:12 GMT
vary
Accept
x-guploader-uploadid
AP6rU81JwqXp4DubtCjOQ_ORKjX5mbf_Ad21qAvHaB3rNTWSdfFYSGPN-brK6-QGxVHeh7Lb
x-cache-status
HIT
cache-control
max-age=31536000, public, max-age=31536000
x-goog-storage-class
STANDARD
via
1.1 google
x-goog-expiration
Fri, 09 Oct 2026 08:18:12 GMT
x-cache-key
/wcsstore/Indraprastha/images/catalog/medium/catalog-image/105/MTA-178175238/no_brand_mystery_box_full01_b7kg1a4y.jpg?w=original:resized:webp
x-upstream-url
image-static-processed-prod.storage.googleapis.com/final-image/medium/catalog-image/105/MTA-178175238/no_brand_mystery_box_full01_b7kg1a4y.webp?authuser=1
accept-ranges
bytes
access-control-allow-origin
https://seller.blibli.com
x-goog-generation
1790324292004114
content-length
8558
x-delivery-format
webp
server
openresty
GET
H2
200
gift_mystery_box_full01_h1xf1r5g.jpg
www.static-src.com/wcsstore/Indraprastha/images/catalog/medium/catalog-image/MTA-178368008/
8 KB
9 KB
366ms
365ms
Image
image/webp
34.117.1.79
Google LLC
General
Full URL
https://www.static-src.com/wcsstore/Indraprastha/images/catalog/medium/catalog-image/MTA-178368008/gift_mystery_box_full01_h1xf1r5g.jpg
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.117.1.79 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
79.1.117.34.bc.googleusercontent.com
Software
openresty /
Resource Hash
c5007d87986fb629a4bc65de165f596febfbe3c2f0e65a88f5a75a1092b4e7e7

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
x-robots-tag
index
x-goog-hash
crc32c=to1BzQ==, md5=gb47EuAqw79r8ppVuT0nkQ==
etag
"81be3b12e02ac3bf6bf29a55b93d2791"
x-goog-stored-content-encoding
identity
x-width-folder
original
expires
Thu, 07 Oct 2027 05:00:07 GMT
alt-svc
h3=":443"; ma=2592000
x-goog-stored-content-length
8558
date
Wed, 07 Oct 2026 05:00:07 GMT
content-type
image/webp
last-modified
Fri, 25 Sep 2026 08:18:12 GMT
vary
Accept
x-guploader-uploadid
AP6rU81gyCUMWSLYgEgxxMw5S_JSlfnYNyiY_nhgMNYyM8OCmgGKrrXIj4hG3M_XPdxdnowTnmhN9qg
x-cache-status
HIT
cache-control
max-age=31536000, public, max-age=31536000
x-goog-storage-class
STANDARD
via
1.1 google
x-goog-expiration
Fri, 09 Oct 2026 08:18:12 GMT
x-cache-key
/wcsstore/Indraprastha/images/catalog/medium/catalog-image/MTA-178368008/gift_mystery_box_full01_h1xf1r5g.jpg?w=original:resized:webp
x-upstream-url
image-static-processed-prod.storage.googleapis.com/final-image/medium/catalog-image/MTA-178368008/gift_mystery_box_full01_h1xf1r5g.webp?authuser=1
accept-ranges
bytes
access-control-allow-origin
https://seller.blibli.com
x-goog-generation
1790324292212739
content-length
8558
x-delivery-format
webp
server
openresty
GET
H3
200
icon-top-rated-diamond.png
www.static-src.com/siva/asset/07_2020/
2 KB
2 KB
547ms
544ms
Image
image/png
34.117.1.79
Google LLC
General
Full URL
https://www.static-src.com/siva/asset/07_2020/icon-top-rated-diamond.png
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
34.117.1.79 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
79.1.117.34.bc.googleusercontent.com
Software
openresty /
Resource Hash
4f41ece4a8b3a961b00908c362d7474dda8cde93ff6f39976454b7137a5ffedd

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
x-robots-tag
index
x-goog-hash
crc32c=eQqiAw==, md5=L6Qit8A6EvWwDOqWjghQuw==
etag
"2fa422b7c03a12f5b00cea968e0850bb"
x-goog-stored-content-encoding
identity
x-width-folder
original
expires
Thu, 07 Oct 2027 05:00:08 GMT
alt-svc
h3=":443"; ma=2592000
x-goog-stored-content-length
1917
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
image/png
last-modified
Mon, 23 Jun 2025 15:49:28 GMT
vary
Accept
x-guploader-uploadid
AP6rU813zudD3dYOWq208IgXUDovEU-xt_MZuaj-G2EwHDr04cjtbuVP9JvWyg0rwzNj9w-ZM1XOAoY
x-cache-status
HIT
cache-control
max-age=31536000, public, max-age=31536000
x-goog-storage-class
STANDARD
via
1.1 google
x-cache-key
/siva/asset/07_2020/icon-top-rated-diamond.png?w=original:resized:png
x-upstream-url
storage.googleapis.com/engagement-services-prod/siva/asset/07_2020/icon-top-rated-diamond.png
accept-ranges
bytes
access-control-allow-origin
https://www.blibli.com
x-goog-generation
1750693768035588
content-length
1917
x-delivery-format
png
server
openresty
GET
H2
200
loader.js Show response
media.flixfacts.com/js/
21 KB
6 KB
314ms
100ms
Script
application/javascript
18.66.122.124
Amazon.com
General
Full URL
https://media.flixfacts.com/js/loader.js
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
18.66.122.124 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-18-66-122-124.fra60.r.cloudfront.net
Software
CloudFront /
Resource Hash
751f56579ad314549bd872256cbb7c3e483630c7da99b03fe324175a242c36c2

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
x-amz-version-id
wRmwnul_pOhxmlAsaevLnx9vv6Ek9dJN
etag
W/"89b3d59f2526a65533307296fe9b8cd7"
age
2226484
access-control-allow-methods
*
x-cache
Hit from cloudfront
x-amz-cf-id
yN_KBa110p3q4QyFcLIIJulO-S3J6BUiF5fx6z9e9KpyO59TuHlhUw==
date
Fri, 11 Sep 2026 10:32:05 GMT
content-type
application/javascript
vary
Accept-Encoding, Origin
last-modified
Fri, 11 Sep 2026 10:28:51 GMT
cache-control
public, max-age=31536000, s-maxage=31536000, immutable
timing-allow-origin
*
via
1.1 1d087f24771eb6834b16162f1bb01660.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-amz-cf-pop
FRA60-P2
server
CloudFront
x-amz-server-side-encryption
AES256
GET
H2
200
/ Show response
media.flixcar.com/modular/js/minify/12612/
689 KB
148 KB
228ms
100ms
Script
text/javascript
18.64.211.128
Amazon.com
General
Full URL
https://media.flixcar.com/modular/js/minify/12612/?url=/clamps/modularvnew/js/service.js&abtesting=1&v=32&ftype=inpage&d=12612&l=id&mpn=749921021090&ean=NUT-60023-01292&brand=Tropicana%20Slim&fl=e2&ssl=1&abtesting=1&ismobile=1&dmn=d3d3LmJsaWJsaS5jb20=&ext=.js
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
18.64.211.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-18-64-211-128.fra56.r.cloudfront.net
Software
CloudFront /
Resource Hash
b0cebe7498636dd05d4a71ebc19036a630a90607694717ba4f96e163dcddadc0

Request headers

Origin
https://daftarslotterpercayaidn.com
sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
60
x-amzn-requestid
92874dc7-ecf3-418c-bdd6-f113d4e0f5e4
x-cache
Hit from cloudfront
x-amz-cf-id
KD0fqXqn-0x3LU-XnjGGqfOVeuAhidb-hm43YIVAeEpM9hhR2gWjPg==
date
Wed, 07 Oct 2026 04:59:07 GMT
content-type
text/javascript;charset=UTF-8
vary
Accept-Encoding
cache-control
public, max-age=2000000, s-maxage=2000000, immutable
timing-allow-origin
*
x-amz-apigw-id
E22wHFCRLPEESAQ=
x-amzn-trace-id
Root=1-6ac5d199-00bfd9897340694544508b79;Parent=56498a82feccb4a4;Sampled=0;Lineage=1:16d39d59:0
via
1.1 8d71893c94b38234ca2b7efa272a14b8.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-amz-cf-pop
FRA56-P16
server
CloudFront
GET
H2
200
rakyatjp-rahasia-jam-gacor-slot-biar-cep-1791348974924-40e3c76a1a82.png
gen.blackmolesamp.com/uploads/
3 MB
3 MB
838ms
385ms
Image
image/png
178.128.116.123
DigitalOcean
General
Full URL
https://gen.blackmolesamp.com/uploads/rakyatjp-rahasia-jam-gacor-slot-biar-cep-1791348974924-40e3c76a1a82.png
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
178.128.116.123 Singapore, Singapore, ASN14061 (DIGITALOCEAN-ASN - DigitalOcean, LLC, US),
Reverse DNS
Software
/ Express
Resource Hash
f3f4ed6781c8e5f84b5a472f9a594dca8c065eed09eb5f2cc7377e7f0ff10556

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
public, max-age=604800
etag
W/"3092b3-1a114b825ed"
via
1.1 Caddy
accept-ranges
bytes
alt-svc
h3=":443"; ma=2592000
content-length
3183283
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
image/png
last-modified
Wed, 07 Oct 2026 04:56:15 GMT
x-powered-by
Express
GET
H3
200
voucher-applied.b1ef57f4.svg
www.static-src.com/frontend/product-detail/static/img/
1 KB
710 B
366ms
363ms
Image
image/svg+xml
34.117.1.79
Google LLC
General
Full URL
https://www.static-src.com/frontend/product-detail/static/img/voucher-applied.b1ef57f4.svg
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
34.117.1.79 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
79.1.117.34.bc.googleusercontent.com
Software
openresty /
Resource Hash
b1ef57f4628064809f0a4d068614c1effab4701076121c3d23d2cca45b9cede3

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
content-encoding
gzip
x-goog-hash
crc32c=k3XP6A==, md5=ctC0i8NRnMBb8/JOAel2tA==
etag
"72d0b48bc3519cc05bf3f24e01e976b4"
x-goog-stored-content-encoding
gzip
expires
Thu, 07 Oct 2027 05:00:07 GMT
alt-svc
h3=":443"; ma=2592000
x-goog-stored-content-length
676
date
Wed, 07 Oct 2026 05:00:07 GMT
content-type
image/svg+xml
vary
Origin
last-modified
Wed, 29 Jul 2026 06:07:22 GMT
x-guploader-uploadid
AP6rU81XtAmsRBogK3NYsUWypAXoyaf3xCYEFsBUcOyBaYgUEcci82XhdJpPt8Fs2pC8R8NT
x-cache-status
HIT
cache-control
max-age=31536000, public
x-goog-storage-class
REGIONAL
via
1.1 google
accept-ranges
bytes
x-goog-generation
1785305242651701
content-length
676
server
openresty
GET
H2
200
index.js Show response
www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/
183 KB
52 KB
1606ms
446ms
Script
application/javascript
34.117.1.79
Google LLC
General
Full URL
https://www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/index.js
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.117.1.79 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
79.1.117.34.bc.googleusercontent.com
Software
openresty /
Resource Hash
a6ef5940d1656af10f49676a33d6dda462853547fa97e9b0231c7d7339cfde3f

Request headers

Origin
https://daftarslotterpercayaidn.com
sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
content-encoding
gzip
x-goog-hash
crc32c=YhYBhw==, md5=4d4IGsn4amJWgDmqkzVfDg==
etag
"e1de081ac9f86a62568039aa93355f0e"
x-goog-stored-content-encoding
gzip
expires
Thu, 07 Oct 2027 05:00:08 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
x-goog-stored-content-length
52950
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
application/javascript
vary
Origin
last-modified
Fri, 30 Aug 2024 15:12:48 GMT
x-guploader-uploadid
AP6rU82dg1wZ5mIcgeSxU1cSXtAOErDSAT9LyWWqJP-wGp7z34G1dQA608HnWGo4mq2f_svGzzke3r0
x-cache-status
MISS
cache-control
max-age=31536000, public
x-goog-storage-class
REGIONAL
via
1.1 google
accept-ranges
bytes
access-control-allow-origin
https://daftarslotterpercayaidn.com
x-goog-generation
1725030768145689
content-length
52950
server
openresty
GET
H2
200
index.css
www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/
474 KB
61 KB
365ms
364ms
Stylesheet
text/css
34.117.1.79
Google LLC
General
Full URL
https://www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/index.css
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.117.1.79 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
79.1.117.34.bc.googleusercontent.com
Software
openresty /
Resource Hash
9f8234eecfdf4dd0cd9783e71222389c7aa2c8382a00c42f4e0326a43e6db96f

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
content-encoding
gzip
x-goog-hash
crc32c=WSP26A==, md5=Esu1l11PA+b+4QynUzDf1w==
etag
"12cbb5975d4f03e6fee10ca75330dfd7"
x-goog-stored-content-encoding
gzip
expires
Thu, 07 Oct 2027 05:00:07 GMT
alt-svc
h3=":443"; ma=2592000
x-goog-stored-content-length
61778
date
Wed, 07 Oct 2026 05:00:07 GMT
content-type
text/css
vary
Origin
last-modified
Fri, 30 Aug 2024 15:12:48 GMT
x-guploader-uploadid
AP6rU82O5rUirL_UI3VYyX00kxIvey4PzzazuP1QQMdEXAhdKRhJSx-tGK-cUgQZ4--2TpNrsJV6jvA
x-cache-status
HIT
cache-control
max-age=31536000, public
x-goog-storage-class
REGIONAL
via
1.1 google
accept-ranges
bytes
x-goog-generation
1725030768036945
content-length
61778
server
openresty
GET
H3
200
GatewayPage.js Show response
www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/js/
76 KB
18 KB
420ms
387ms
Script
application/javascript
34.117.1.79
Google LLC
General
Full URL
https://www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/js/GatewayPage.js
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
34.117.1.79 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
79.1.117.34.bc.googleusercontent.com
Software
openresty /
Resource Hash
6e9d1c8da726584f12acb23c3345d00715a7e08476b834b8694301b51f3ebec0

Request headers

Origin
https://daftarslotterpercayaidn.com
sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
content-encoding
gzip
x-goog-hash
crc32c=V/MbtQ==, md5=RUmyigLdvkQKEe4kKdGUyQ==
etag
"4549b28a02ddbe440a11ee2429d194c9"
x-goog-stored-content-encoding
gzip
expires
Thu, 07 Oct 2027 05:00:07 GMT
alt-svc
h3=":443"; ma=2592000
x-goog-stored-content-length
18843
date
Wed, 07 Oct 2026 05:00:07 GMT
content-type
application/javascript
vary
Origin
last-modified
Fri, 30 Aug 2024 15:12:59 GMT
x-guploader-uploadid
AP6rU810EqohcCW7ogNauHdlrEAP8hK9bCOZJBqMsvnqdFa4XdPVCE46O2EYGqvAbiTEzR8m9fgpOLw
x-cache-status
MISS
cache-control
max-age=31536000, public
x-goog-storage-class
REGIONAL
via
1.1 google
accept-ranges
bytes
access-control-allow-origin
https://daftarslotterpercayaidn.com
x-goog-generation
1725030779344739
content-length
18843
server
openresty
GET
H3
200
product-id-mixin.js Show response
www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/js/
977 B
462 B
384ms
384ms
Script
application/javascript
34.117.1.79
Google LLC
General
Full URL
https://www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/js/product-id-mixin.js
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
34.117.1.79 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
79.1.117.34.bc.googleusercontent.com
Software
openresty /
Resource Hash
bf7f8eafeefe4b116ebd7e3e2b82f077e749b186f1605b3ca86c647ecbc6ed6c

Request headers

Origin
https://daftarslotterpercayaidn.com
sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
content-encoding
gzip
x-goog-hash
crc32c=3S+ijg==, md5=MBZ0+aP3Igp0NCYJMPONQQ==
etag
"301674f9a3f7220a7434260930f38d41"
x-goog-stored-content-encoding
gzip
expires
Thu, 07 Oct 2027 05:00:07 GMT
alt-svc
h3=":443"; ma=2592000
x-goog-stored-content-length
428
date
Wed, 07 Oct 2026 05:00:07 GMT
content-type
application/javascript
vary
Origin
last-modified
Fri, 30 Aug 2024 15:12:56 GMT
x-guploader-uploadid
AP6rU81bdy2cj-gMKRzUHKScy9R_GafkGBltgReTW-HO6PTFNXDon5SBzy-CntU4bdWgBQs
x-cache-status
MISS
cache-control
max-age=31536000, public
x-goog-storage-class
REGIONAL
via
1.1 google
accept-ranges
bytes
access-control-allow-origin
https://daftarslotterpercayaidn.com
x-goog-generation
1725030776171055
content-length
428
server
openresty
GET

summary-mixin.js
www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/js/
0
0


GET
H3
200
referrer-mixin.js Show response
www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/js/
370 B
290 B
388ms
383ms
Script
application/javascript
34.117.1.79
Google LLC
General
Full URL
https://www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/js/referrer-mixin.js
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
34.117.1.79 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
79.1.117.34.bc.googleusercontent.com
Software
openresty /
Resource Hash
bf3f4f2ee6a19afb6e25e733a283990dcbdbbdd9ab1d6bb4dcd1e2962065a07a

Request headers

Origin
https://daftarslotterpercayaidn.com
sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
content-encoding
gzip
x-goog-hash
crc32c=IPAHXA==, md5=1hXOfIFBiqOBVm/QMKz+zQ==
etag
"d615ce7c81418aa381566fd030acfecd"
x-goog-stored-content-encoding
gzip
expires
Thu, 07 Oct 2027 05:00:07 GMT
alt-svc
h3=":443"; ma=2592000
x-goog-stored-content-length
258
date
Wed, 07 Oct 2026 05:00:07 GMT
content-type
application/javascript
vary
Origin
last-modified
Fri, 30 Aug 2024 15:12:54 GMT
x-guploader-uploadid
AP6rU818NO0cjTwkiBBNBDua29CvOe40SBGp9SuDfwVlcmvOfZRWiwJ1ymhn13C-xB6LtYZl20kneZM
x-cache-status
MISS
cache-control
max-age=31536000, public
x-goog-storage-class
REGIONAL
via
1.1 google
accept-ranges
bytes
access-control-allow-origin
https://daftarslotterpercayaidn.com
x-goog-generation
1725030774495553
content-length
258
server
openresty
GET
H3
200
DetailPage.js Show response
www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/js/
63 KB
19 KB
388ms
383ms
Script
application/javascript
34.117.1.79
Google LLC
General
Full URL
https://www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/js/DetailPage.js
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
34.117.1.79 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
79.1.117.34.bc.googleusercontent.com
Software
openresty /
Resource Hash
a8784ee846c1266bed7cab511a9814e89273945fdfae2cadf0dc26c4cf97c601

Request headers

Origin
https://daftarslotterpercayaidn.com
sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
content-encoding
gzip
x-goog-hash
crc32c=mln8wg==, md5=9S7dbevXXzwmpR91W2RALQ==
etag
"f52edd6debd75f3c26a51f755b64402d"
x-goog-stored-content-encoding
gzip
expires
Thu, 07 Oct 2027 05:00:07 GMT
alt-svc
h3=":443"; ma=2592000
x-goog-stored-content-length
19260
date
Wed, 07 Oct 2026 05:00:07 GMT
content-type
application/javascript
vary
Origin
last-modified
Fri, 30 Aug 2024 15:13:00 GMT
x-guploader-uploadid
AP6rU820xAUcJQ33ehGPRPQBRgJO1iFGHxV56kUr7sbdzTeLZmp6-5LKWqdzAVydTiE5L6I
x-cache-status
MISS
cache-control
max-age=31536000, public
x-goog-storage-class
REGIONAL
via
1.1 google
accept-ranges
bytes
access-control-allow-origin
https://daftarslotterpercayaidn.com
x-goog-generation
1725030780220231
content-length
19260
server
openresty
GET
H3
404
companion.js
daftarslotterpercayaidn.com/sw/companion/v1/
0
0
229ms
226ms
Script
text/html
172.67.155.237
Cloudflare
General
Full URL
https://daftarslotterpercayaidn.com/sw/companion/v1/companion.js
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.67.155.237 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
cache-control
max-age=14400
content-encoding
zstd
cf-cache-status
HIT
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=3bsVz99KVZr6REqc0SE7CsCUTsnL7PnwFVh8dJFimE7VcJ6Fja%2FGl71seFVq7H19h1NQ0CM9dVsP%2BQKGcHOoZzwP3D8nY%2Bo8YTvv2yUEf6A2C0As1YL%2FndBoEUUre5X0g1iY%2FuNjNjK9pWKC80I%3D"}]}
cf-ray
a46a57245f259d75-WAW
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Wed, 07 Oct 2026 05:00:07 GMT
last-modified
Sun, 12 Jul 2026 01:01:40 GMT
content-type
text/html
server
cloudflare
priority
u=3,i=?0
GET
H2
200
gtm.js Show response
www.googletagmanager.com/
757 KB
209 KB
301ms
186ms
Script
application/javascript
192.178.183.97
Google LLC
General
Full URL
https://www.googletagmanager.com/gtm.js?id=GTM-TKQZL95
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
192.178.183.97 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfraw-in-f97.1e100.net
Software
Google Tag Manager /
Resource Hash
597e9639dbadba00680015f321c3b4acfcbe8cb47f0e61420dcae4d09e391af8
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
zstd
expires
Wed, 07 Oct 2026 05:00:08 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
last-modified
Wed, 07 Oct 2026 03:00:00 GMT
access-control-allow-headers
Cache-Control
strict-transport-security
max-age=31536000; includeSubDomains
cache-control
private, max-age=900
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
access-control-allow-origin
*
content-length
213515
x-xss-protection
0
server
Google Tag Manager
GET
H2
200
adsct
t.co/1/i/
43 B
672 B
238ms
169ms
Image
image/gif
172.66.0.227
Cloudflare
General
Full URL
https://t.co/1/i/adsct?bci=4&eci=3&event=%7B%7D&event_id=e6c078f3-a76e-42b7-adcd-bbafdc7a71f9&integration=advertiser&p_id=Twitter&p_user_id=0&pl_id=e861ccc9-118a-4c87-a238-c52cf85cc919&tw_document_href=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FmetaData%3D4eHyfurj4yL7Q4Ucv84uGYHJb0g2t%2BFdwECMb3QsHNjtAqmaWkaBfGgt5w9qTEikAP03CsR8aLRQodyhRwzA9w%3D%3D%26pickupPointCode%3DPP-3495802&tw_iframe_status=0&txn_id=nvqtr&type=javascript&version=2.3.30
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.66.0.227 , United States, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare envoy /
Resource Hash
ac8778041fdb7f2e08ceb574c9a766247ea26f1a7d90fa854c4efcf4b361a957
Security Headers
Name Value
Strict-Transport-Security max-age=631138519; includeSubdomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=631138519; includeSubdomains
x-transaction-id
4a58fb40123d56d1
cache-control
no-cache, no-store, max-age=0
origin-cf-ray
a46a5725cbcc6338-WAW
cf-cache-status
DYNAMIC
cf-ray
a46a5725cbcc6338-WAW
x-response-time
6
content-length
43
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
image/gif;charset=utf-8
perf
7402827104
server
cloudflare envoy
x-served-by
t4_a
GET
H2
200
adsct
analytics.twitter.com/1/i/
43 B
816 B
260ms
187ms
Image
image/gif
172.66.0.227
Cloudflare
General
Full URL
https://analytics.twitter.com/1/i/adsct?bci=4&eci=3&event=%7B%7D&event_id=e6c078f3-a76e-42b7-adcd-bbafdc7a71f9&integration=advertiser&p_id=Twitter&p_user_id=0&pl_id=e861ccc9-118a-4c87-a238-c52cf85cc919&tw_document_href=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FmetaData%3D4eHyfurj4yL7Q4Ucv84uGYHJb0g2t%2BFdwECMb3QsHNjtAqmaWkaBfGgt5w9qTEikAP03CsR8aLRQodyhRwzA9w%3D%3D%26pickupPointCode%3DPP-3495802&tw_iframe_status=0&txn_id=nvqtr&type=javascript&version=2.3.30
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.66.0.227 , United States, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare envoy /
Resource Hash
ac8778041fdb7f2e08ceb574c9a766247ea26f1a7d90fa854c4efcf4b361a957
Security Headers
Name Value
Strict-Transport-Security max-age=631138519; includeSubdomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=631138519; includeSubdomains
x-transaction-id
692d2576ecaa69b3
cache-control
no-cache, no-store, max-age=0
origin-cf-ray
a46a5725e9f51607-WAW
cf-cache-status
DYNAMIC
cf-ray
a46a5725e9f51607-WAW
x-response-time
6
content-length
43
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
image/gif;charset=utf-8
perf
7402827104
server
cloudflare envoy
x-served-by
t4_a
GET
H2
200
lt.min.js Show response
tags.crwdcntrl.net/lt/c/10867/
66 KB
20 KB
254ms
101ms
Script
text/javascript
18.66.102.77
Amazon.com
General
Full URL
https://tags.crwdcntrl.net/lt/c/10867/lt.min.js
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
18.66.102.77 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-18-66-102-77.fra56.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
b24be3f1a44e12d12428e08feb1f043434035af652507659715dd944d26c3262

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding
cache-control
public, max-age=86400
content-encoding
gzip
etag
W/"49c0bc8a67e83d2c46b87e8d43dc787d"
age
37944
via
1.1 c2e56cd54e2593df95ccca8a6d98c958.cloudfront.net (CloudFront)
alt-svc
h3=":443"; ma=86400
x-cache
Hit from cloudfront
x-amz-cf-id
33lt1bAkgl-QHoHBR6DJN3LGhEfmQgwcTYTOoxbEpwCULZ3_EyKLYw==
date
Tue, 06 Oct 2026 18:27:44 GMT
content-type
text/javascript
last-modified
Wed, 13 May 2026 17:46:48 GMT
server
AmazonS3
x-amz-cf-pop
FRA56-P2
x-amz-server-side-encryption
AES256
GET
H3
200
7082.js Show response
script.crazyegg.com/pages/scripts/0075/
9 KB
3 KB
44ms
42ms
Script
text/javascript
104.19.147.8
Cloudflare
General
Full URL
https://script.crazyegg.com/pages/scripts/0075/7082.js
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.19.147.8 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
e2f36a32e1ba4787a3391b7a670fa43a9bec7431f4823774344b68c398eed905

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

access-control-expose-headers
CE-Version
content-encoding
gzip
cf-cache-status
HIT
age
3439
server-timing
cfExtPri
alt-svc
h3=":443"; ma=86400
date
Wed, 07 Oct 2026 05:00:07 GMT
content-type
text/javascript
last-modified
Wed, 07 Oct 2026 04:02:48 GMT
vary
accept-encoding
priority
u=3,i=?0
cache-control
public, max-age=300, s-maxage=1209600
timing-allow-origin
*
cf-ray
a46a5724587ebf47-WAW
accept-ranges
bytes
access-control-allow-origin
*
content-length
3105
ce-version
11.5.557
server
cloudflare
GET
H2
200
adsct
t.co/1/i/
43 B
475 B
181ms
180ms
Image
image/gif
172.66.0.227
Cloudflare
General
Full URL
https://t.co/1/i/adsct?bci=4&eci=4&event=%7B%22currency%22%3A%22IDR%22%2C%22contents%22%3A%5B%7B%22content_id%22%3A%22NUT-60023-01292-00001%22%2C%22content_name%22%3A%22Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%22%2C%22content_price%22%3A343900%2C%22num_items%22%3A1%7D%5D%7D&event_id=4ca2e880-e25e-4c70-802d-0b2bd0f156ce&integration=advertiser&p_id=Twitter&p_user_id=0&pl_id=e861ccc9-118a-4c87-a238-c52cf85cc919&tw_document_href=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&tw_iframe_status=0&txn_id=tw-nvqtr-ocmzu&type=javascript&version=2.3.30
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.66.0.227 , United States, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare envoy /
Resource Hash
ac8778041fdb7f2e08ceb574c9a766247ea26f1a7d90fa854c4efcf4b361a957
Security Headers
Name Value
Strict-Transport-Security max-age=631138519; includeSubdomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=631138519; includeSubdomains
x-transaction-id
93a405ac6504c622
cache-control
no-cache, no-store, max-age=0
origin-cf-ray
a46a5725ebeb6338-WAW
cf-cache-status
DYNAMIC
cf-ray
a46a5725ebeb6338-WAW
x-response-time
6
content-length
43
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
image/gif;charset=utf-8
perf
7402827104
server
cloudflare envoy
x-served-by
t4_a
GET
H2
200
adsct
analytics.twitter.com/1/i/
43 B
1009 B
160ms
158ms
Image
image/gif
172.66.0.227
Cloudflare
General
Full URL
https://analytics.twitter.com/1/i/adsct?bci=4&eci=4&event=%7B%22currency%22%3A%22IDR%22%2C%22contents%22%3A%5B%7B%22content_id%22%3A%22NUT-60023-01292-00001%22%2C%22content_name%22%3A%22Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%22%2C%22content_price%22%3A343900%2C%22num_items%22%3A1%7D%5D%7D&event_id=4ca2e880-e25e-4c70-802d-0b2bd0f156ce&integration=advertiser&p_id=Twitter&p_user_id=0&pl_id=e861ccc9-118a-4c87-a238-c52cf85cc919&tw_document_href=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&tw_iframe_status=0&txn_id=tw-nvqtr-ocmzu&type=javascript&version=2.3.30
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.66.0.227 , United States, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare envoy /
Resource Hash
ac8778041fdb7f2e08ceb574c9a766247ea26f1a7d90fa854c4efcf4b361a957
Security Headers
Name Value
Strict-Transport-Security max-age=631138519; includeSubdomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=631138519; includeSubdomains
x-transaction-id
1e02abf9220f73c6
cache-control
no-cache, no-store, max-age=0
origin-cf-ray
a46a5725e9f71607-WAW
cf-cache-status
DYNAMIC
cf-ray
a46a5725e9f71607-WAW
x-response-time
6
content-length
43
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
image/gif;charset=utf-8
perf
7402827104
server
cloudflare envoy
x-served-by
t4_a
GET
H2
200
adsct
t.co/1/i/
43 B
478 B
209ms
209ms
Image
image/gif
172.66.0.227
Cloudflare
General
Full URL
https://t.co/1/i/adsct?bci=4&eci=4&event=%7B%22currency%22%3A%22IDR%22%2C%22contents%22%3A%5B%7B%22content_id%22%3A%22NUT-60023-01292-00001%22%2C%22content_name%22%3A%22Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%22%2C%22content_price%22%3A343900%2C%22num_items%22%3A1%7D%5D%7D&event_id=f30339de-5ed8-4e40-8882-65e41f9ce731&integration=advertiser&p_id=Twitter&p_user_id=0&pl_id=e861ccc9-118a-4c87-a238-c52cf85cc919&tw_document_href=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&tw_iframe_status=0&txn_id=tw-nvqtr-ocmzu&type=javascript&version=2.3.30
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.66.0.227 , United States, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare envoy /
Resource Hash
ac8778041fdb7f2e08ceb574c9a766247ea26f1a7d90fa854c4efcf4b361a957
Security Headers
Name Value
Strict-Transport-Security max-age=631138519; includeSubdomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=631138519; includeSubdomains
x-transaction-id
3b1e2d2d598315c8
cache-control
no-cache, no-store, max-age=0
origin-cf-ray
a46a57262c3f6338-WAW
cf-cache-status
DYNAMIC
cf-ray
a46a57262c3f6338-WAW
x-response-time
8
content-length
43
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
image/gif;charset=utf-8
perf
7402827104
server
cloudflare envoy
x-served-by
t4_a
GET
H2
200
adsct
analytics.twitter.com/1/i/
43 B
823 B
168ms
166ms
Image
image/gif
172.66.0.227
Cloudflare
General
Full URL
https://analytics.twitter.com/1/i/adsct?bci=4&eci=4&event=%7B%22currency%22%3A%22IDR%22%2C%22contents%22%3A%5B%7B%22content_id%22%3A%22NUT-60023-01292-00001%22%2C%22content_name%22%3A%22Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%22%2C%22content_price%22%3A343900%2C%22num_items%22%3A1%7D%5D%7D&event_id=f30339de-5ed8-4e40-8882-65e41f9ce731&integration=advertiser&p_id=Twitter&p_user_id=0&pl_id=e861ccc9-118a-4c87-a238-c52cf85cc919&tw_document_href=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&tw_iframe_status=0&txn_id=tw-nvqtr-ocmzu&type=javascript&version=2.3.30
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.66.0.227 , United States, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare envoy /
Resource Hash
ac8778041fdb7f2e08ceb574c9a766247ea26f1a7d90fa854c4efcf4b361a957
Security Headers
Name Value
Strict-Transport-Security max-age=631138519; includeSubdomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=631138519; includeSubdomains
x-transaction-id
da99ed43976f7d24
cache-control
no-cache, no-store, max-age=0
origin-cf-ray
a46a57263a721607-WAW
cf-cache-status
DYNAMIC
cf-ray
a46a57263a721607-WAW
x-response-time
12
content-length
43
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
image/gif;charset=utf-8
perf
7402827104
server
cloudflare envoy
x-served-by
t4_a
GET
H2
200
v8c78df7c7c0f484497ecbca7046644da1771523124516 Show response
static.cloudflareinsights.com/beacon.min.js/
30 KB
11 KB
119ms
58ms
Script
text/javascript
104.16.80.73
Cloudflare
General
Full URL
https://static.cloudflareinsights.com/beacon.min.js/v8c78df7c7c0f484497ecbca7046644da1771523124516
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.16.80.73 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
4b77eae349a8cbcea7133cf3640a64ebf1f69d54d8f6469d7be6fdc188ca4ca4

Request headers

Origin
https://daftarslotterpercayaidn.com
sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
public, max-age=86400
content-encoding
gzip
etag
W/"2026.2.0"
cross-origin-resource-policy
cross-origin
cf-ray
a46a5726cb7ce5d7-WAW
access-control-allow-origin
*
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
text/javascript;charset=UTF-8
last-modified
Mon, 05 Oct 2026 15:56:55 GMT
server
cloudflare
GET
H2
200
v833ccba57c9e4d2798f2e76cebdd09a11778172276447 Show response
static.cloudflareinsights.com/beacon.min.js/
32 KB
11 KB
39ms
38ms
Script
text/javascript
104.16.80.73
Cloudflare
General
Full URL
https://static.cloudflareinsights.com/beacon.min.js/v833ccba57c9e4d2798f2e76cebdd09a11778172276447
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.16.80.73 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
aca73fc574e12740e3368860b88a284d01b643456f3ed6a06322ecb47750563f

Request headers

Origin
https://daftarslotterpercayaidn.com
sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
public, max-age=86400
content-encoding
gzip
etag
W/"2026.5.0"
cross-origin-resource-policy
cross-origin
cf-ray
a46a5726cb84e5d7-WAW
access-control-allow-origin
*
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
text/javascript;charset=UTF-8
last-modified
Mon, 05 Oct 2026 15:56:55 GMT
server
cloudflare
GET
H2
200
v4513226cdae34746b4dedf0b4dfa099e1781791509496 Show response
static.cloudflareinsights.com/beacon.min.js/
31 KB
11 KB
73ms
72ms
Script
text/javascript
104.16.80.73
Cloudflare
General
Full URL
https://static.cloudflareinsights.com/beacon.min.js/v4513226cdae34746b4dedf0b4dfa099e1781791509496
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
104.16.80.73 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
e1ac4849b9d4a498b68f8aca01e6ed99a11d94b35a2cec533b3916b8fb722fd6

Request headers

Origin
https://daftarslotterpercayaidn.com
sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
public, max-age=86400
content-encoding
gzip
etag
W/"2026.6.0"
cross-origin-resource-policy
cross-origin
cf-ray
a46a5726dba1e5d7-WAW
access-control-allow-origin
*
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
text/javascript;charset=UTF-8
last-modified
Mon, 05 Oct 2026 15:56:55 GMT
server
cloudflare
GET
H2
200
e.gif
dev.visualwebsiteoptimizer.com/
35 B
208 B
175ms
173ms
Image
image/gif
34.107.218.251
Google LLC
General
Full URL
https://dev.visualwebsiteoptimizer.com/e.gif?f=https%3A%2F%2Fdev.visualwebsiteoptimizer.com%2F7.0%2Fva-42b830ab1f45f2a5aa737b55d5e9e251.js&l=25&c=129561&a=undefined&s=uncaughtErr&e=Uncaught%20TypeError%3A%20Cannot%20read%20properties%20of%20undefined%20(reading%20%27sv%27)&stack=TypeError%3A%20Cannot%20read%20properties%20of%20undefined%20(reading%20%27sv%27)%0A%20%20%20%20at%20https%3A%2F%2Fdev.visualwebsiteoptimizer.com%2F7.0%2Fva-42b830ab1f45f2a5aa737b55d5e9e251.js%3A25%3A129561%0A%20%20%20%20at%20https%3A%2F%2Fdev.visualwebsiteoptimizer.com%2F7.0%2Fva-42b830ab1f45f2a5aa737b55d5e9e251.js%3A25%3A193653%0A%20%20%20%20at%20https%3A%2F%2Fdev.visualwebsiteoptimizer.com%2F7.0%2Fva-42b830ab1f45f2a5aa737b55d5e9e251.js%3A25%3A193656&vn=7.0&vns=undefined&vno=undefined&_cu=https%3A%2F%2Fdaftarslotterpercayaidn.com%2F&eTime=1791349207689&random=0.01549721828324313
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.107.218.251 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
251.218.107.34.bc.googleusercontent.com
Software
gnv03c /
Resource Hash
8337212354871836e6763a41e615916c89bac5b3f1f0adf60ba43c7c806e1015
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains; preload
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000; includeSubDomains; preload
cache-control
private, no-cache, no-cache=Set-Cookie, proxy-revalidate
pragma
no-cache
x-content-type-options
nosniff
via
1.1 google
expires
Mon, 10 Jan 2005 00:00:01 GMT
access-control-allow-origin
*
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
35
date
Wed, 07 Oct 2026 05:00:07 GMT
content-type
image/gif
server
gnv03c
POST
H2
200
live Show response
sdk-01.moengage.com/v1/experiences/web/
128 B
749 B
189ms
188ms
XHR
application/json
3.161.82.25
Amazon.com
General
Full URL
https://sdk-01.moengage.com/v1/experiences/web/live?
Requested by
Host: cdn.moengage.com
URL: https://cdn.moengage.com/release/dc_1/moe_webSdk_webp.min.latest.js?app_id=QTD7QXC51X5DZR3CTIHK33PQ
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.25 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-25.fra56.r.cloudfront.net
Software
envoy /
Resource Hash
86406a30f04aa2e75cf60409fe44ab1b557b827d3ae413d68164cdc82ecb9082

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
MOE-APPKEY
QTD7QXC51X5DZR3CTIHK33PQ
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
Content-Type
application/json
sec-ch-ua-mobile
?0
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36

Response headers

content-encoding
gzip
access-control-allow-methods
GET, POST, OPTIONS, DELETE, PUT, PATCH
x-cache
Miss from cloudfront
moe-request-id
vAJrsrTe
x-amz-cf-id
Z2No0Zkq17n5f3lsTJ8waEPaozMGJOqO-rHzYaIjrAk575WdDUnc7A==
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
application/json
access-control-allow-headers
DNT, User-Agent, X-Requested-With, If-Modified-Since,Cache-Control, Content-Type, Range, MOE-DBNAME, MOE-APPKEY,MOE-REQUEST-ID, MOE-UNIQUE-ID, MOE-APPSECRET, MOE-INAPP-BATCH-ID, MOE-DASHBOARD-USER-ID, Authorization
x-envoy-upstream-service-time
12
x-ratelimit-reset
52
via
1.1 3c13cc51908e4d37d2a5046d7703e256.cloudfront.net (CloudFront)
x-ratelimit-remaining
9740
access-control-allow-origin
*
content-length
107
x-ratelimit-limit
10000, 10000;w=60
x-amz-cf-pop
FRA56-P10
server
envoy
OPTIONS
H2
200
live
sdk-01.moengage.com/v1/experiences/web/ Frame
0
0
310ms
166ms
Preflight
application/json
3.161.82.25
Amazon.com
General
Full URL
https://sdk-01.moengage.com/v1/experiences/web/live?
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.25 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-25.fra56.r.cloudfront.net
Software
envoy /
Resource Hash

Request headers

Accept
*/*
Access-Control-Request-Headers
content-type,moe-appkey
Access-Control-Request-Method
POST
Origin
https://daftarslotterpercayaidn.com
Sec-Fetch-Mode
cors
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36

Response headers

access-control-allow-headers
DNT, User-Agent, X-Requested-With, If-Modified-Since,Cache-Control, Content-Type, Range, MOE-DBNAME, MOE-APPKEY,MOE-REQUEST-ID, MOE-UNIQUE-ID, MOE-APPSECRET, MOE-INAPP-BATCH-ID, MOE-DASHBOARD-USER-ID, Authorization
access-control-allow-methods
GET, POST, OPTIONS, DELETE, PUT, PATCH
access-control-allow-origin
*
content-length
0
content-type
application/json
date
Wed, 07 Oct 2026 05:00:07 GMT
moe-request-id
SmAvLNVr
server
envoy
via
1.1 3c13cc51908e4d37d2a5046d7703e256.cloudfront.net (CloudFront)
x-amz-cf-id
3QHfcHJc5JatLPqDHfStLIBhYJTl-q5GNALLRth7_BsNODH2Strz_w==
x-amz-cf-pop
FRA56-P10
x-cache
Miss from cloudfront
x-envoy-upstream-service-time
3
GET

blibli-medium-eee84661.woff2
www.static-src.com/frontend/static/fonts/
0
0


GET

blibli-demi-bold-6dd433a2.woff2
www.static-src.com/frontend/static/fonts/
0
0


GET
H3
200
iconrakyatjp.webp
meubelkayumurah.pics/wp-content/uploads/2026/05/
2 KB
3 KB
36ms
35ms
Image
image/webp
188.114.97.3
Cloudflare
General
Full URL
https://meubelkayumurah.pics/wp-content/uploads/2026/05/iconrakyatjp.webp
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
188.114.97.3 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
3064c443efe71ba06a3aa0a60a29fb67ed9b49a55597a61b2f23eb345567ffb3

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=14400
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
cf-cache-status
HIT
age
1816
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=DV1urVIWRADSsRlmxZsbcxVvq4Eypshq6oeuPtYAcwiKBtgqdzvhF9lEeVf%2FNfidEm9LNFi8CcrbdbM6Kysk6WaHd5Ni6qsGZIddWJGD5SUh42iaVSlCi2Xjmk%2FIi9AkDGu5RVJF7g%3D%3D"}]}
cf-ray
a46a57249991cf5c-WAW
accept-ranges
bytes
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
content-length
2334
date
Wed, 07 Oct 2026 05:00:07 GMT
content-type
image/webp
last-modified
Mon, 18 May 2026 11:14:58 GMT
server
cloudflare
priority
u=3,i
GET
H2
200
/
www.google.pl/pagead/1p-conversion/880395410/
Redirect Chain
  • https://googleads.g.doubleclick.net/pagead/viewthroughconversion/880395410/?random=1232230327&cv=11&fst=1726498673589&bg=ffffff&guid=ON&async=1&gtm=45be4990v877689920z8810058345za201zb810058345&gcd...
  • https://www.google.com/pagead/1p-conversion/880395410/?random=1232230327&cv=11&fst=1726498673589&bg=ffffff&guid=ON&async=1&gtm=45be4990v877689920z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&t...
  • https://www.google.pl/pagead/1p-conversion/880395410/?random=1232230327&cv=11&fst=1726498673589&bg=ffffff&guid=ON&async=1&gtm=45be4990v877689920z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&ta...
42 B
108 B
138ms
137ms
Image
image/gif
142.251.110.94
Google LLC
General
Full URL
https://www.google.pl/pagead/1p-conversion/880395410/?random=1232230327&cv=11&fst=1726498673589&bg=ffffff&guid=ON&async=1&gtm=45be4990v877689920z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&label=hEx3CKjo-eADEJKJ56MD&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&value=0&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&capi=1&fmt=3&ct_cookie_present=false&crd=CLTesQII8t-xAgit4bECCK_hsQIIobixAgixwbECCLDBsQIIscOxAgiKxbECCMLJsQII1-ixAgi0xrECCIfbsQII08WxAgjrzLECCO3OsQII1c-xAgj02rECCOLqsQII6O6xAgiS67ECCMnjsQIIl9SxAgjJ27ECCM3msQIIpt2xAgiw3rECCIDbsQIIzeGxAgjL4bEC&cerd=ChCDsL4tueu-LZPuvi2d6bc4&fsk=ChEI8LiS1gYQmNSM96yGof7IARIsACm40NJaAiKra6_dnSoP2qLNJ2J5R14ZFm1sfuVTK71_QDZBXmF1nNUBdAoaAusQ&is_vtc=1&cid=CAQSXgBAziHcij5-FVbyy6156t-CWbN26tl0nU81PFVDh2QcEXv3mPmPYPHEmkqDXcbhAqRtHRVmOXWsuLx8OmEQTMbOmU7-9Dp8iyEGAuxSppXBuasNUVxyagfBXgqjJYo&eitems=ChEI8LiS1gYQ-Y_IobO6hrHxARIdAPOWweHHVOk-UMg9I8Km92jpbhxAfM5AOHxJZNg&random=574239686&ipr=y&pscrd=IhMI-NrM6Y-nlwMVyiZ7BB24TA1COiRodHRwczovL2RhZnRhcnNsb3R0ZXJwZXJjYXlhaWRuLmNvbS9CWENoRUk4TGlTMWdZUXM0djJ6YVdfdzl2UEFSSXRBQXVYbGhyYkUzeUZlN3dMNG8ySG9lSmE4d1Z2Snhra3FvWkV6STMxRkxrWDdYS3RyQ3FiU3V5MGRLeXZ6DAgJYggIABAAGAAgAA
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Server
142.251.110.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f94.1e100.net
Software
cafe /
Resource Hash
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
Security Headers
Name Value
Content-Security-Policy script-src 'none'; object-src 'none'
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
Referer
https://daftarslotterpercayaidn.com/

Response headers

content-security-policy
script-src 'none'; object-src 'none'
cache-control
no-cache, no-store, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
42
date
Wed, 07 Oct 2026 05:00:08 GMT
x-xss-protection
0
content-type
image/gif
server
cafe

Redirect headers

content-security-policy
script-src 'none'; object-src 'none'
cache-control
no-cache, no-store, must-revalidate
timing-allow-origin
*
location
https://www.google.pl/pagead/1p-conversion/880395410/?random=1232230327&cv=11&fst=1726498673589&bg=ffffff&guid=ON&async=1&gtm=45be4990v877689920z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&label=hEx3CKjo-eADEJKJ56MD&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&value=0&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&capi=1&fmt=3&ct_cookie_present=false&crd=CLTesQII8t-xAgit4bECCK_hsQIIobixAgixwbECCLDBsQIIscOxAgiKxbECCMLJsQII1-ixAgi0xrECCIfbsQII08WxAgjrzLECCO3OsQII1c-xAgj02rECCOLqsQII6O6xAgiS67ECCMnjsQIIl9SxAgjJ27ECCM3msQIIpt2xAgiw3rECCIDbsQIIzeGxAgjL4bEC&cerd=ChCDsL4tueu-LZPuvi2d6bc4&fsk=ChEI8LiS1gYQmNSM96yGof7IARIsACm40NJaAiKra6_dnSoP2qLNJ2J5R14ZFm1sfuVTK71_QDZBXmF1nNUBdAoaAusQ&is_vtc=1&cid=CAQSXgBAziHcij5-FVbyy6156t-CWbN26tl0nU81PFVDh2QcEXv3mPmPYPHEmkqDXcbhAqRtHRVmOXWsuLx8OmEQTMbOmU7-9Dp8iyEGAuxSppXBuasNUVxyagfBXgqjJYo&eitems=ChEI8LiS1gYQ-Y_IobO6hrHxARIdAPOWweHHVOk-UMg9I8Km92jpbhxAfM5AOHxJZNg&random=574239686&ipr=y&pscrd=IhMI-NrM6Y-nlwMVyiZ7BB24TA1COiRodHRwczovL2RhZnRhcnNsb3R0ZXJwZXJjYXlhaWRuLmNvbS9CWENoRUk4TGlTMWdZUXM0djJ6YVdfdzl2UEFSSXRBQXVYbGhyYkUzeUZlN3dMNG8ySG9lSmE4d1Z2Snhra3FvWkV6STMxRkxrWDdYS3RyQ3FiU3V5MGRLeXZ6DAgJYggIABAAGAAgAA
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
42
date
Wed, 07 Oct 2026 05:00:08 GMT
x-xss-protection
0
content-type
image/gif
server
cafe
GET
H3
200
/
www.google.com/pagead/1p-user-list/925089264/
42 B
64 B
104ms
55ms
Image
image/gif
142.251.156.119
Google LLC
General
Full URL
https://www.google.com/pagead/1p-user-list/925089264/?random=1726498673524&cv=11&fst=1726495200000&bg=ffffff&guid=ON&async=1&gtm=45be4990z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=ecomm_pagetype%3Dproduct%3Becomm_prodid%3DNUT-60023-01292%3Becomm_totalvalue%3D343900&rfmt=3&fmt=3&is_vtc=1&cid=CAQSUABAziHcZwWgITdceSDnj09gjsyI73q72rywpoqMWBOzPn5P2NE3yWZoTlmJTl91UX4Y2wRFe4nXuASk4KR7weeLFBBMt8HiRmXkQK4qaMDq&random=472540497&rmt_tld=0&ipr=y
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.156.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
cafe /
Resource Hash
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
Security Headers
Name Value
Content-Security-Policy script-src 'none'; object-src 'none'
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-security-policy
script-src 'none'; object-src 'none'
cache-control
no-cache, no-store, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
42
date
Wed, 07 Oct 2026 05:00:08 GMT
x-xss-protection
0
content-type
image/gif
server
cafe
GET
H2
200
/
www.google.pl/pagead/1p-user-list/925089264/
42 B
455 B
172ms
65ms
Image
image/gif
142.251.110.94
Google LLC
General
Full URL
https://www.google.pl/pagead/1p-user-list/925089264/?random=1726498673524&cv=11&fst=1726495200000&bg=ffffff&guid=ON&async=1&gtm=45be4990z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=ecomm_pagetype%3Dproduct%3Becomm_prodid%3DNUT-60023-01292%3Becomm_totalvalue%3D343900&rfmt=3&fmt=3&is_vtc=1&cid=CAQSUABAziHcZwWgITdceSDnj09gjsyI73q72rywpoqMWBOzPn5P2NE3yWZoTlmJTl91UX4Y2wRFe4nXuASk4KR7weeLFBBMt8HiRmXkQK4qaMDq&random=472540497&rmt_tld=1&ipr=y
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.110.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f94.1e100.net
Software
cafe /
Resource Hash
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
Security Headers
Name Value
Content-Security-Policy script-src 'none'; object-src 'none'
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-security-policy
script-src 'none'; object-src 'none'
cache-control
no-cache, no-store, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
42
date
Wed, 07 Oct 2026 05:00:08 GMT
x-xss-protection
0
content-type
image/gif
server
cafe
GET
H3
200
/
www.google.com/pagead/1p-user-list/880395410/
42 B
64 B
95ms
55ms
Image
image/gif
142.251.156.119
Google LLC
General
Full URL
https://www.google.com/pagead/1p-user-list/880395410/?random=1726498671571&cv=11&fst=1726495200000&bg=ffffff&guid=ON&async=1&gtm=45je4990v877689920z8810058345za200zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FmetaData%3D4eHyfurj4yL7Q4Ucv84uGYHJb0g2t%2BFdwECMb3QsHNjtAqmaWkaBfGgt5w9qTEikAP03CsR8aLRQodyhRwzA9w%3D%3D%26pickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Online%20Mall%20Blibli.com%2C%20Sensasi%20Belanja%20Online%20Shop%20ala%20Mall&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=event%3Dgtag.config&rfmt=3&fmt=3&is_vtc=1&cid=CAQSUABAziHcE3439mT0WloYXBTvV4xwirjb_a4PVfPE2s7tGPPg-09nKf0UIvIVydgMsTHNHtIZgDiAhD65bnHRYF5xoOJshv9lRpfklVuU3IFZ&random=4288350285&rmt_tld=0&ipr=y
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.156.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
cafe /
Resource Hash
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
Security Headers
Name Value
Content-Security-Policy script-src 'none'; object-src 'none'
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-security-policy
script-src 'none'; object-src 'none'
cache-control
no-cache, no-store, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
42
date
Wed, 07 Oct 2026 05:00:08 GMT
x-xss-protection
0
content-type
image/gif
server
cafe
GET
H2
200
/
www.google.pl/pagead/1p-user-list/880395410/
42 B
108 B
180ms
74ms
Image
image/gif
142.251.110.94
Google LLC
General
Full URL
https://www.google.pl/pagead/1p-user-list/880395410/?random=1726498671571&cv=11&fst=1726495200000&bg=ffffff&guid=ON&async=1&gtm=45je4990v877689920z8810058345za200zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FmetaData%3D4eHyfurj4yL7Q4Ucv84uGYHJb0g2t%2BFdwECMb3QsHNjtAqmaWkaBfGgt5w9qTEikAP03CsR8aLRQodyhRwzA9w%3D%3D%26pickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Online%20Mall%20Blibli.com%2C%20Sensasi%20Belanja%20Online%20Shop%20ala%20Mall&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=event%3Dgtag.config&rfmt=3&fmt=3&is_vtc=1&cid=CAQSUABAziHcE3439mT0WloYXBTvV4xwirjb_a4PVfPE2s7tGPPg-09nKf0UIvIVydgMsTHNHtIZgDiAhD65bnHRYF5xoOJshv9lRpfklVuU3IFZ&random=4288350285&rmt_tld=1&ipr=y
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.110.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f94.1e100.net
Software
cafe /
Resource Hash
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
Security Headers
Name Value
Content-Security-Policy script-src 'none'; object-src 'none'
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-security-policy
script-src 'none'; object-src 'none'
cache-control
no-cache, no-store, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
42
date
Wed, 07 Oct 2026 05:00:08 GMT
x-xss-protection
0
content-type
image/gif
server
cafe
GET
H3
200
/
www.google.com/pagead/1p-user-list/920334631/
42 B
64 B
78ms
53ms
Image
image/gif
142.251.156.119
Google LLC
General
Full URL
https://www.google.com/pagead/1p-user-list/920334631/?random=1726498673536&cv=11&fst=1726495200000&bg=ffffff&guid=ON&async=1&gtm=45be4990z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=ecomm_pagetype%3Dretail-product-detail%3Becomm_prodid%3DNUT-60023-01292%3Becomm_totalvalue%3D343900&rfmt=3&fmt=3&is_vtc=1&cid=CAQSUABAziHcu6oezOLWt_wGv1KzJ8o02UtdL5BclG-buq_80BVVX8VRokg3eqY6coDha634n-BpbaCBVOAqQxLruW2tnI3uw6W2preO9bY23YYu&random=1865439814&rmt_tld=0&ipr=y
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.156.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
cafe /
Resource Hash
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
Security Headers
Name Value
Content-Security-Policy script-src 'none'; object-src 'none'
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-security-policy
script-src 'none'; object-src 'none'
cache-control
no-cache, no-store, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
42
date
Wed, 07 Oct 2026 05:00:08 GMT
x-xss-protection
0
content-type
image/gif
server
cafe
GET
H2
200
/
www.google.pl/pagead/1p-user-list/920334631/
42 B
108 B
154ms
66ms
Image
image/gif
142.251.110.94
Google LLC
General
Full URL
https://www.google.pl/pagead/1p-user-list/920334631/?random=1726498673536&cv=11&fst=1726495200000&bg=ffffff&guid=ON&async=1&gtm=45be4990z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=ecomm_pagetype%3Dretail-product-detail%3Becomm_prodid%3DNUT-60023-01292%3Becomm_totalvalue%3D343900&rfmt=3&fmt=3&is_vtc=1&cid=CAQSUABAziHcu6oezOLWt_wGv1KzJ8o02UtdL5BclG-buq_80BVVX8VRokg3eqY6coDha634n-BpbaCBVOAqQxLruW2tnI3uw6W2preO9bY23YYu&random=1865439814&rmt_tld=1&ipr=y
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.110.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f94.1e100.net
Software
cafe /
Resource Hash
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
Security Headers
Name Value
Content-Security-Policy script-src 'none'; object-src 'none'
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-security-policy
script-src 'none'; object-src 'none'
cache-control
no-cache, no-store, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
42
date
Wed, 07 Oct 2026 05:00:08 GMT
x-xss-protection
0
content-type
image/gif
server
cafe
GET
H3
200
/
www.google.com/pagead/1p-user-list/925089264/
42 B
64 B
73ms
55ms
Image
image/gif
142.251.156.119
Google LLC
General
Full URL
https://www.google.com/pagead/1p-user-list/925089264/?random=1726498714047&cv=11&fst=1726495200000&bg=ffffff&guid=ON&async=1&gtm=45be4990z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1024&u_h=824&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=ecomm_pagetype%3Dproduct%3Becomm_prodid%3DNUT-60023-01292%3Becomm_totalvalue%3D343900&rfmt=3&fmt=3&is_vtc=1&cid=CAQSXgBAziHcf9hBWpyXJxrI8lvdfWw8N7l5wO9dVJ8SzE-VgYgBDNaoKgsjk2Y4aGPTdFNvKNCDR0TXsuI1ym12qCfCU68xD6hzfIlifqwJO-zE9DwUX9J7ByWc7HIR8Ts&random=3194029588&rmt_tld=0&ipr=y
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.156.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
cafe /
Resource Hash
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
Security Headers
Name Value
Content-Security-Policy script-src 'none'; object-src 'none'
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-security-policy
script-src 'none'; object-src 'none'
cache-control
no-cache, no-store, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
42
date
Wed, 07 Oct 2026 05:00:08 GMT
x-xss-protection
0
content-type
image/gif
server
cafe
GET
H2
200
/
www.google.pl/pagead/1p-user-list/925089264/
42 B
108 B
123ms
65ms
Image
image/gif
142.251.110.94
Google LLC
General
Full URL
https://www.google.pl/pagead/1p-user-list/925089264/?random=1726498714047&cv=11&fst=1726495200000&bg=ffffff&guid=ON&async=1&gtm=45be4990z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1024&u_h=824&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=ecomm_pagetype%3Dproduct%3Becomm_prodid%3DNUT-60023-01292%3Becomm_totalvalue%3D343900&rfmt=3&fmt=3&is_vtc=1&cid=CAQSXgBAziHcf9hBWpyXJxrI8lvdfWw8N7l5wO9dVJ8SzE-VgYgBDNaoKgsjk2Y4aGPTdFNvKNCDR0TXsuI1ym12qCfCU68xD6hzfIlifqwJO-zE9DwUX9J7ByWc7HIR8Ts&random=3194029588&rmt_tld=1&ipr=y
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.110.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f94.1e100.net
Software
cafe /
Resource Hash
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
Security Headers
Name Value
Content-Security-Policy script-src 'none'; object-src 'none'
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-security-policy
script-src 'none'; object-src 'none'
cache-control
no-cache, no-store, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
42
date
Wed, 07 Oct 2026 05:00:08 GMT
x-xss-protection
0
content-type
image/gif
server
cafe
GET
H3
200
/
www.google.com/pagead/1p-user-list/920334631/
42 B
64 B
55ms
55ms
Image
image/gif
142.251.156.119
Google LLC
General
Full URL
https://www.google.com/pagead/1p-user-list/920334631/?random=1726498714059&cv=11&fst=1726495200000&bg=ffffff&guid=ON&async=1&gtm=45be4990z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1024&u_h=824&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=ecomm_pagetype%3Dretail-product-detail%3Becomm_prodid%3DNUT-60023-01292%3Becomm_totalvalue%3D343900&rfmt=3&fmt=3&is_vtc=1&cid=CAQSXgBAziHc5Ak2ekYMfTHN-QQSwAHTxVIK3SYVoO4u0sShLS2eonXJw35hCqTgv1NUG3--J_SKifiPdXZHfSw4w3fUR0NPHIyjsJiEQTO-6iVUvmHCfcAfZbi2vMWUMA0&random=4246067202&rmt_tld=0&ipr=y
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.156.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
cafe /
Resource Hash
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
Security Headers
Name Value
Content-Security-Policy script-src 'none'; object-src 'none'
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-security-policy
script-src 'none'; object-src 'none'
cache-control
no-cache, no-store, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
42
date
Wed, 07 Oct 2026 05:00:08 GMT
x-xss-protection
0
content-type
image/gif
server
cafe
GET
H2
200
/
www.google.pl/pagead/1p-user-list/920334631/
42 B
108 B
77ms
66ms
Image
image/gif
142.251.110.94
Google LLC
General
Full URL
https://www.google.pl/pagead/1p-user-list/920334631/?random=1726498714059&cv=11&fst=1726495200000&bg=ffffff&guid=ON&async=1&gtm=45be4990z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1024&u_h=824&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=ecomm_pagetype%3Dretail-product-detail%3Becomm_prodid%3DNUT-60023-01292%3Becomm_totalvalue%3D343900&rfmt=3&fmt=3&is_vtc=1&cid=CAQSXgBAziHc5Ak2ekYMfTHN-QQSwAHTxVIK3SYVoO4u0sShLS2eonXJw35hCqTgv1NUG3--J_SKifiPdXZHfSw4w3fUR0NPHIyjsJiEQTO-6iVUvmHCfcAfZbi2vMWUMA0&random=4246067202&rmt_tld=1&ipr=y
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.110.94 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
bz-in-f94.1e100.net
Software
cafe /
Resource Hash
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
Security Headers
Name Value
Content-Security-Policy script-src 'none'; object-src 'none'
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-security-policy
script-src 'none'; object-src 'none'
cache-control
no-cache, no-store, must-revalidate
timing-allow-origin
*
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-content-type-options
nosniff
expires
Fri, 01 Jan 1990 00:00:00 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
p3p
policyref="https://www.googleadservices.com/pagead/p3p.xml", CP="NOI DEV PSA PSD IVA IVD OTP OUR OTR IND OTC"
content-length
42
date
Wed, 07 Oct 2026 05:00:08 GMT
x-xss-protection
0
content-type
image/gif
server
cafe
GET
H2
200
/ Show response
media.flixcar.com/modular/js/minify/12612/
689 KB
148 KB
55ms
54ms
Script
text/javascript
18.64.211.128
Amazon.com
General
Full URL
https://media.flixcar.com/modular/js/minify/12612/?url=/clamps/modularvnew/js/service.js&v=32&ftype=inpage&d=12612&l=id&mpn=749921021090&ean=NUT-60023-01292&brand=Tropicana%20Slim&fl=e2&ssl=1&dmn=ZGFmdGFyc2xvdHRlcnBlcmNheWFpZG4uY29t&ext=.js
Requested by
Host: media.flixfacts.com
URL: https://media.flixfacts.com/js/loader.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
18.64.211.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-18-64-211-128.fra56.r.cloudfront.net
Software
CloudFront /
Resource Hash
b0cebe7498636dd05d4a71ebc19036a630a90607694717ba4f96e163dcddadc0

Request headers

Origin
https://daftarslotterpercayaidn.com
sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
br
age
61
x-amzn-requestid
92874dc7-ecf3-418c-bdd6-f113d4e0f5e4
x-cache
Hit from cloudfront
x-amz-cf-id
bq5FSH5sYfdcp2c_ruzVmV4Iic6P5EnlMotoqQ2IjkjMMKIuSYutrg==
date
Wed, 07 Oct 2026 04:59:07 GMT
content-type
text/javascript;charset=UTF-8
vary
Accept-Encoding
cache-control
public, max-age=2000000, s-maxage=2000000, immutable
timing-allow-origin
*
x-amz-apigw-id
E22wHFCRLPEESAQ=
x-amzn-trace-id
Root=1-6ac5d199-00bfd9897340694544508b79;Parent=56498a82feccb4a4;Sampled=0;Lineage=1:16d39d59:0
via
1.1 8d71893c94b38234ca2b7efa272a14b8.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-amz-cf-pop
FRA56-P16
server
CloudFront
POST
H2
204
collect
region1.google-analytics.com/g/
0
0
136ms
58ms
Fetch
text/plain
216.239.34.36
Google LLC
General
Full URL
https://region1.google-analytics.com/g/collect?v=2&tid=G-SF0EQEXKPW&gtm=45je6a51v9197814496za200zd9197814496xf1&_p=1791349207709&gcd=13l3l3l2l1l1&npa=1&dma_cps=a&dma=1&cid=501682970.1791349208&frm=0&ngs=1&pscdl=noapi&rcb=13&sr=1600x1200&uaa=x86&uab=64&uafvl=Chromium%3B154.0.8037.97%7CGoogle%2520Chrome%3B154.0.8037.97%7CNot%2520A(Brand%3B99.0.0.0&uam=&uamb=0&uap=Linux&uapv=&uaw=0&ul=pl-pl&_s=1&tag_exp=115938466~115938469~118897920~118897930~120213116~120385422~120469145~120469153~121046263~121046271~121280969&sid=1791349208&sct=1&seg=0&dl=https%3A%2F%2Fdaftarslotterpercayaidn.com%2F&dt=RAKYATJP%3A%20Rahasia%20Jam%20Gacor%20Slot%20Biar%20Cepat%20Maxwin&en=page_view&_fv=1&_nsi=1&_ss=1&_ee=1&tfd=1890
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtag/js?id=G-SF0EQEXKPW
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
216.239.34.36 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
Golfe2 /
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache, no-store, must-revalidate
pragma
no-cache
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
content-security-policy-report-only
script-src 'none'; form-action 'none'; frame-src 'none'; report-uri https://csp.withgoogle.com/csp/scaffolding/ascnsrsggc:141:0
report-to
{"group":"ascnsrsggc:141:0","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/scaffolding/ascnsrsggc:141:0"}],}
expires
Fri, 01 Jan 1990 00:00:00 GMT
access-control-allow-origin
https://daftarslotterpercayaidn.com
cross-origin-opener-policy-report-only
same-origin; report-to=ascnsrsggc:141:0
content-length
0
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
text/plain
server
Golfe2
POST
H2
200
live Show response
sdk-01.moengage.com/v1/experiences/web/
128 B
750 B
176ms
175ms
XHR
application/json
3.161.82.25
Amazon.com
General
Full URL
https://sdk-01.moengage.com/v1/experiences/web/live?
Requested by
Host: cdn.moengage.com
URL: https://cdn.moengage.com/release/dc_1/moe_webSdk_webp.min.latest.js?app_id=QTD7QXC51X5DZR3CTIHK33PQ
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.25 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-25.fra56.r.cloudfront.net
Software
envoy /
Resource Hash
86406a30f04aa2e75cf60409fe44ab1b557b827d3ae413d68164cdc82ecb9082

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
MOE-APPKEY
QTD7QXC51X5DZR3CTIHK33PQ
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
Content-Type
application/json
sec-ch-ua-mobile
?0
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36

Response headers

content-encoding
gzip
access-control-allow-methods
GET, POST, OPTIONS, DELETE, PUT, PATCH
x-cache
Miss from cloudfront
moe-request-id
tFljqOJO
x-amz-cf-id
OBO8-W0FF8mNBcUwIxEcqPm3WkytdObfIR08MoUTIbyFyVC-v3daWQ==
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
application/json
access-control-allow-headers
DNT, User-Agent, X-Requested-With, If-Modified-Since,Cache-Control, Content-Type, Range, MOE-DBNAME, MOE-APPKEY,MOE-REQUEST-ID, MOE-UNIQUE-ID, MOE-APPSECRET, MOE-INAPP-BATCH-ID, MOE-DASHBOARD-USER-ID, Authorization
x-envoy-upstream-service-time
13
x-ratelimit-reset
52
via
1.1 3c13cc51908e4d37d2a5046d7703e256.cloudfront.net (CloudFront)
x-ratelimit-remaining
9734
access-control-allow-origin
*
content-length
107
x-ratelimit-limit
10000, 10000;w=60
x-amz-cf-pop
FRA56-P10
server
envoy
GET
H3
200
blibli-medium-eee84661.woff2
www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/fonts/
70 KB
71 KB
393ms
392ms
Font
application/octet-stream
34.117.1.79
Google LLC
General
Full URL
https://www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/fonts/blibli-medium-eee84661.woff2
Requested by
Host: www.static-src.com
URL: https://www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/index.css
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
34.117.1.79 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
79.1.117.34.bc.googleusercontent.com
Software
openresty /
Resource Hash
eee84661a5d29de16948e34abed935317718666412654a2a0fd753b0db7c6971

Request headers

Origin
https://daftarslotterpercayaidn.com
sec-ch-ua-platform
"Linux"
Referer
https://www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/index.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
content-encoding
gzip
x-goog-hash
crc32c=zj1+2A==, md5=71LD98qTrmX5a7StLwkceg==
etag
"ef52c3f7ca93ae65f96bb4ad2f091c7a"
x-goog-stored-content-encoding
gzip
expires
Thu, 07 Oct 2027 05:00:08 GMT
alt-svc
h3=":443"; ma=2592000
x-goog-stored-content-length
72161
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
application/octet-stream
vary
Origin
last-modified
Fri, 30 Aug 2024 15:13:01 GMT
x-guploader-uploadid
AP6rU81tHGUb2mtXcjqTSq-UUJbPjfeE5LVeRqwAcsWTIsRwPD4rd6cEBqOjS1-2fkny9UZ5qDCw8ek
x-cache-status
MISS
cache-control
max-age=31536000, public
x-goog-storage-class
REGIONAL
via
1.1 google
accept-ranges
bytes
access-control-allow-origin
https://daftarslotterpercayaidn.com
x-goog-generation
1725030781834817
content-length
72161
server
openresty
GET
H2
200
C-H-I-C-K.png
i.ibb.co.com/FCYH409/
169 KB
170 KB
217ms
88ms
Image
image/png
45.43.142.8
OVH OVH SAS
General
Full URL
https://i.ibb.co.com/FCYH409/C-H-I-C-K.png
Requested by
Host: www.static-src.com
URL: https://www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/index.css
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
45.43.142.8 , United Kingdom, ASN16276 (OVH OVH SAS, FR),
Reverse DNS
Software
openresty /
Resource Hash
985fa323ed22e810b311c5d7032cbef87f2a377ee0b217b8d13a544cf034c3ef

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.static-src.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=315360000, public
access-control-allow-methods
GET, OPTIONS
expires
Thu, 31 Dec 2037 23:55:55 GMT
accept-ranges
bytes
access-control-allow-origin
*
content-length
173134
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
image/png
last-modified
Tue, 30 Jun 2026 15:50:55 GMT
server
openresty
GET
H3
200
blibli-demi-bold-6dd433a2.woff2
www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/fonts/
70 KB
71 KB
389ms
388ms
Font
application/octet-stream
34.117.1.79
Google LLC
General
Full URL
https://www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/fonts/blibli-demi-bold-6dd433a2.woff2
Requested by
Host: www.static-src.com
URL: https://www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/index.css
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
34.117.1.79 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
79.1.117.34.bc.googleusercontent.com
Software
openresty /
Resource Hash
6dd433a2e6f5626e3a794f2bd1688efb5bb59cdbae73d8b224d773875422a6d2

Request headers

Origin
https://daftarslotterpercayaidn.com
sec-ch-ua-platform
"Linux"
Referer
https://www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/index.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
content-encoding
gzip
x-goog-hash
crc32c=XOVwWw==, md5=/+xXSzr44uu08hqgxcNUtg==
etag
"ffec574b3af8e2ebb4f21aa0c5c354b6"
x-goog-stored-content-encoding
gzip
expires
Thu, 07 Oct 2027 05:00:08 GMT
alt-svc
h3=":443"; ma=2592000
x-goog-stored-content-length
71997
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
application/octet-stream
vary
Origin
last-modified
Fri, 30 Aug 2024 15:13:01 GMT
x-guploader-uploadid
AP6rU83pSZf7X2fDGaL7pAddXW-oasE6_z4cletSMjcISJdY9ru4PuN-pLdZQPnaTynztuKg
x-cache-status
MISS
cache-control
max-age=31536000, public
x-goog-storage-class
REGIONAL
via
1.1 google
accept-ranges
bytes
access-control-allow-origin
https://daftarslotterpercayaidn.com
x-goog-generation
1725030781800258
content-length
71997
server
openresty
GET
H3
200
promo-highlight-blue.7bdc38da.png
www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/img/
7 KB
7 KB
361ms
361ms
Image
image/png
34.117.1.79
Google LLC
General
Full URL
https://www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/img/promo-highlight-blue.7bdc38da.png
Requested by
Host: www.static-src.com
URL: https://www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/index.css
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
34.117.1.79 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
79.1.117.34.bc.googleusercontent.com
Software
openresty /
Resource Hash
7bdc38dabd16b72f068e78906e2ab7374ff0525a29a8855d8e3a5fbb7901a21d

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/index.css
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
x-goog-hash
crc32c=LaK5Uw==, md5=549YUGNShAh3BIUL4dg0Cw==
x-goog-stored-content-encoding
gzip
expires
Thu, 07 Oct 2027 05:00:08 GMT
alt-svc
h3=":443"; ma=2592000
x-goog-stored-content-length
6868
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
image/png
vary
Origin,Accept-Encoding
last-modified
Fri, 30 Aug 2024 15:13:01 GMT
x-guploader-uploadid
AP6rU80LXh86JBIU_ynnqrG_bHaFeM4cDk4lEkoUxl2nks4O7ir3RdXigIz9tsdXwQS_YMGH4LySBIU
x-cache-status
HIT
cache-control
max-age=31536000, public
x-goog-storage-class
REGIONAL
via
1.1 google
x-goog-generation
1725030781687773
server
openresty
GET
H2
200
uwt.js Show response
static.ads-twitter.com/
61 KB
17 KB
167ms
52ms
Script
application/javascript
146.75.120.157
Fastly
General
Full URL
https://static.ads-twitter.com/uwt.js
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
146.75.120.157 Frankfurt am Main, Germany, ASN54113 (FASTLY - Fastly, Inc., US),
Reverse DNS
Software
/
Resource Hash
8968e2907b8936778ed050dd55d8ef7232b3d32ee95b1f7122b4dfa9e22c4839

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

vary
Accept-Encoding,Host
cache-control
no-cache
content-encoding
gzip
etag
"8f378d7f2e96ebc7d4f49c02d1a11dd2+gzip+gzip"
accept-ranges
bytes
x-cache
HIT, HIT
p3p
CP="CAO DSP LAW CURa ADMa DEVa TAIa PSAa PSDa IVAa IVDa OUR BUS IND UNI COM NAV INT"
content-length
17310
date
Wed, 07 Oct 2026 05:00:08 GMT
x-tw-cdn
FT
last-modified
Fri, 18 Sep 2026 23:07:03 GMT
content-type
application/javascript; charset=utf-8
x-served-by
cache-iad-kiad7000083-IAD, cache-fra-etou8220103-FRA
x-amz-server-side-encryption
AES256
GET
H3
200
fbevents.js Show response
connect.facebook.net/en_US/
419 KB
110 KB
51ms
50ms
Script
application/x-javascript
57.144.244.128
Facebook
General
Full URL
https://connect.facebook.net/en_US/fbevents.js
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
57.144.244.128 Frankfurt am Main, Germany, ASN32934 (FACEBOOK - Facebook, Inc., US),
Reverse DNS
xx-fbcdn-shv-01-fra5.fbcdn.net
Software
/
Resource Hash
89a2a82574d35ba44820a985fff208cb50bbe810307f7ee069f97fd391c9a131
Security Headers
Name Value
Content-Security-Policy default-src *.facebook.com *.fbcdn.net *.facebook.net 'self' blob:;script-src *.facebook.com *.fbcdn.net *.facebook.net blob: 'self' 'nonce-TxPjkH0N';style-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob: 'unsafe-inline';connect-src *.facebook.com facebook.com *.fbcdn.net *.facebook.net wss://*.facebook.com:* wss://*.fbcdn.net attachment.fbsbx.com *.cdninstagram.com blob: 'self' data: https://edge-chat.facebook.net https://edge-chat-latest.facebook.net wss://edge-chat-latest.facebook.net wss://edge-chat.facebook.net wss://edge-chat.socialplugin.facebook.net wss://edge-chat-latest.socialplugin.facebook.net https://edge-chat.socialplugin.facebook.net https://edge-chat-latest.socialplugin.facebook.net;font-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;img-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;media-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;child-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;frame-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;manifest-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;object-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;worker-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;block-all-mixed-content;upgrade-insecure-requests;report-uri https://www.facebook.com/csp/reporting/?m=c&minimize=0;
Strict-Transport-Security max-age=31536000; preload; includeSubDomains
X-Content-Type-Options nosniff
X-Frame-Options DENY
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
report-to
{"max_age":2592000,"endpoints":[{"url":"https:\/\/www.facebook.com\/browser_reporting\/coop\/?minimize=0"}],"group":"coop_report","include_subdomains":true}, {"max_age":86400,"endpoints":[{"url":"https:\/\/www.facebook.com\/browser_reporting\/coep\/?minimize=0"}],"group":"coep_report"}, {"max_age":21600,"endpoints":[{"url":"https:\/\/www.facebook.com\/ajax\/browser_error_reports\/"}],"group":"permissions_policy"}
x-content-type-options
nosniff
expires
Sat, 01 Jan 2000 00:00:00 GMT
alt-svc
h3=":443"; ma=86400
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
application/x-javascript; charset=utf-8
vary
Accept-Encoding
cross-origin-embedder-policy-report-only
require-corp;report-to="coep_report"
priority
u=3,i
x-frame-options
DENY
strict-transport-security
max-age=31536000; preload; includeSubDomains
reporting-endpoints
coop_report="https://www.facebook.com/browser_reporting/coop/?minimize=0", coep_report="https://www.facebook.com/browser_reporting/coep/?minimize=0", permissions_policy="https://www.facebook.com/ajax/browser_error_reports/"
content-security-policy
default-src *.facebook.com *.fbcdn.net *.facebook.net 'self' blob:;script-src *.facebook.com *.fbcdn.net *.facebook.net blob: 'self' 'nonce-TxPjkH0N';style-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob: 'unsafe-inline';connect-src *.facebook.com facebook.com *.fbcdn.net *.facebook.net wss://*.facebook.com:* wss://*.fbcdn.net attachment.fbsbx.com *.cdninstagram.com blob: 'self' data: https://edge-chat.facebook.net https://edge-chat-latest.facebook.net wss://edge-chat-latest.facebook.net wss://edge-chat.facebook.net wss://edge-chat.socialplugin.facebook.net wss://edge-chat-latest.socialplugin.facebook.net https://edge-chat.socialplugin.facebook.net https://edge-chat-latest.socialplugin.facebook.net;font-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;img-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;media-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;child-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;frame-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;manifest-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;object-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;worker-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;block-all-mixed-content;upgrade-insecure-requests;report-uri https://www.facebook.com/csp/reporting/?m=c&minimize=0;
cache-control
public, max-age=1200
timing-allow-origin
*
cross-origin-opener-policy
same-origin-allow-popups
x-fb-connection-quality
EXCELLENT; q=0.9, rtt=48, rtx=0, c=103, mss=1232, tbw=112039, tp=104, tpl=0, uplat=0, ullat=-1
pragma
public
x-fb-debug
FbJaH5wjKGm6+1QCohFSH1yUaGLMaFANNotp0Dr0KMT5Ii9PoDzgBXnWFUqg0UMKEurCEq6Ti9Xy5x7pzitgCQ==
cross-origin-resource-policy
cross-origin
permissions-policy
accelerometer=(), attribution-reporting=(), autoplay=(), bluetooth=(), camera=(), ch-device-memory=(), ch-downlink=(), ch-dpr=(), ch-ect=(), ch-rtt=(), ch-save-data=(), ch-ua-arch=(), ch-ua-bitness=(), ch-viewport-height=(), ch-viewport-width=(), ch-width=(), clipboard-read=(), clipboard-write=(), compute-pressure=(), display-capture=(), encrypted-media=(), fullscreen=(self), gamepad=(), geolocation=(), gyroscope=(), hid=(), idle-detection=(), interest-cohort=(), keyboard-map=(), local-fonts=(), magnetometer=(), microphone=(), midi=(), otp-credentials=(), payment=(), picture-in-picture=(), private-state-token-issuance=(), publickey-credentials-get=(), screen-wake-lock=(), serial=(), shared-storage=(), shared-storage-select-url=(), private-state-token-redemption=(), usb=(), unload=(self), window-management=(), xr-spatial-tracking=();report-to="permissions_policy"
document-policy
force-load-at-top, include-js-call-stacks-in-crash-reports
content-length
112721
x-xss-protection
0
origin-agent-cluster
?1
GET
H2
404
880395410 Show response
td.doubleclick.net/td/rul/ Frame 75DE
2 KB
2 KB
286ms
146ms
Document
text/html
142.251.14.157
Google LLC
General
Full URL
https://td.doubleclick.net/td/rul/880395410?random=1726498671571&cv=11&fst=1726498671571&fmt=3&bg=ffffff&guid=ON&async=1&gtm=45je4990v877689920z8810058345za200zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FmetaData%3D4eHyfurj4yL7Q4Ucv84uGYHJb0g2t%2BFdwECMb3QsHNjtAqmaWkaBfGgt5w9qTEikAP03CsR8aLRQodyhRwzA9w%3D%3D%26pickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Online%20Mall%20Blibli.com%2C%20Sensasi%20Belanja%20Online%20Shop%20ala%20Mall&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=event%3Dgtag.config
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.14.157 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f157.1e100.net
Software
/
Resource Hash
bd15337dca5ab822c0f983145a7428b0449b5387de2104f7a5a3c6bb4348767f

Request headers

Referer
https://daftarslotterpercayaidn.com/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
1577
content-type
text/html; charset=UTF-8
date
Wed, 07 Oct 2026 05:00:08 GMT
referrer-policy
no-referrer
GET
H2
204
tags
asia.creativecdn.com/ Frame CC01
Redirect Chain
  • https://asia.creativecdn.com/tags?id=pr_FAOiA95ZI30AXifJGDUt_offer_NUT-60023-01292-00001&id=pr_FAOiA95ZI30AXifJGDUt_uid_unknown
  • https://asia.creativecdn.com/tags?id=pr_FAOiA95ZI30AXifJGDUt_offer_NUT-60023-01292-00001&id=pr_FAOiA95ZI30AXifJGDUt_uid_unknown&tc=1
0
0
398ms
397ms
Document
text/plain
103.132.192.30
RTB HOUSE PTE. LTD.
General
Full URL
https://asia.creativecdn.com/tags?id=pr_FAOiA95ZI30AXifJGDUt_offer_NUT-60023-01292-00001&id=pr_FAOiA95ZI30AXifJGDUt_uid_unknown&tc=1
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
103.132.192.30 , Singapore, ASN138552 (RTBHOUSE-AS-AP - RTB HOUSE PTE. LTD., SG),
Reverse DNS
ip-103-132-192-30.rtbhouse.net
Software
/
Resource Hash

Request headers

Referer
https://daftarslotterpercayaidn.com/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

Redirect headers

access-control-allow-credentials
true
access-control-allow-methods
GET, POST
access-control-allow-origin
*
access-control-max-age
3600
cache-control
no-cache, no-store, must-revalidate, private, max-age=0
content-length
0
date
Wed, 07 Oct 2026 05:00:09 GMT
expires
Thu, 01 Jan 1970 00:00:00 GMT Thu, 01 Jan 1970 00:00:00 GMT
location
https://asia.creativecdn.com/tags?id=pr_FAOiA95ZI30AXifJGDUt_offer_NUT-60023-01292-00001&id=pr_FAOiA95ZI30AXifJGDUt_uid_unknown&tc=1
p3p
CP="NON DSP COR CURa PSA PSD OUR BUS NAV STA"
pragma
no-cache
vary
Origin
GET
H2
200
tracker.js Show response
c.o-s.io/115069/
47 KB
8 KB
276ms
103ms
Script
application/javascript
18.66.147.45
Amazon.com
General
Full URL
https://c.o-s.io/115069/tracker.js
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
18.66.147.45 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-18-66-147-45.fra60.r.cloudfront.net
Software
AmazonS3 /
Resource Hash
1877334064592aa3d57f28dd4eef88800dd67d81c5654e2520de1107cad36932

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=3600, public, must-revalidate
content-encoding
gzip
etag
W/"611f49fb2985152333d18170da71c23c"
age
1053
via
1.1 12e62b05f63a1a2118cca20014b15012.cloudfront.net (CloudFront)
x-cache
Hit from cloudfront
x-amz-cf-id
o_o_NNejruk0CqUtZIaYjhC6JFtj4RPdIG5O9FYdcLNNiGbcRqFjKg==
date
Wed, 07 Oct 2026 04:46:01 GMT
content-type
application/javascript
last-modified
Fri, 11 Jun 2021 10:45:48 GMT
server
AmazonS3
x-amz-cf-pop
FRA60-P4
vary
Accept-Encoding
GET
H2
404
925089264 Show response
td.doubleclick.net/td/rul/ Frame 7923
2 KB
2 KB
261ms
162ms
Document
text/html
142.251.14.157
Google LLC
General
Full URL
https://td.doubleclick.net/td/rul/925089264?random=1726498673524&cv=11&fst=1726498673524&fmt=3&bg=ffffff&guid=ON&async=1&gtm=45be4990z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=ecomm_pagetype%3Dproduct%3Becomm_prodid%3DNUT-60023-01292%3Becomm_totalvalue%3D343900
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.14.157 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f157.1e100.net
Software
/
Resource Hash
980ed2ca9a1e43c42e0d94a927fc79f3e07c62d0b9623501a2b8015d04948222

Request headers

Referer
https://daftarslotterpercayaidn.com/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
1577
content-type
text/html; charset=UTF-8
date
Wed, 07 Oct 2026 05:00:08 GMT
referrer-policy
no-referrer
GET
H2
404
920334631 Show response
td.doubleclick.net/td/rul/ Frame A779
2 KB
2 KB
247ms
149ms
Document
text/html
142.251.14.157
Google LLC
General
Full URL
https://td.doubleclick.net/td/rul/920334631?random=1726498673536&cv=11&fst=1726498673536&fmt=3&bg=ffffff&guid=ON&async=1&gtm=45be4990z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=ecomm_pagetype%3Dretail-product-detail%3Becomm_prodid%3DNUT-60023-01292%3Becomm_totalvalue%3D343900
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.14.157 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f157.1e100.net
Software
/
Resource Hash
5f2badb55c07c25d970b453e5650df9ce4e86a6ca5b6f8a96f7041b73b9210ba

Request headers

Referer
https://daftarslotterpercayaidn.com/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
1577
content-type
text/html; charset=UTF-8
date
Wed, 07 Oct 2026 05:00:08 GMT
referrer-policy
no-referrer
GET
H2
404
880395410 Show response
td.doubleclick.net/td/rul/ Frame B6F7
2 KB
2 KB
244ms
147ms
Document
text/html
142.251.14.157
Google LLC
General
Full URL
https://td.doubleclick.net/td/rul/880395410?random=1726498673589&cv=11&fst=1726498673589&fmt=3&bg=ffffff&guid=ON&async=1&gtm=45be4990v877689920z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&label=hEx3CKjo-eADEJKJ56MD&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&value=0&bttype=purchase&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&capi=1&ct_cookie_present=0
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.14.157 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f157.1e100.net
Software
/
Resource Hash
bd15337dca5ab822c0f983145a7428b0449b5387de2104f7a5a3c6bb4348767f

Request headers

Referer
https://daftarslotterpercayaidn.com/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
1577
content-type
text/html; charset=UTF-8
date
Wed, 07 Oct 2026 05:00:08 GMT
referrer-policy
no-referrer
GET
H2
204
tags
asia.creativecdn.com/ Frame EDD6
Redirect Chain
  • https://asia.creativecdn.com/tags?id=pr_FAOiA95ZI30AXifJGDUt_offer_NUT-60023-01292-00001&id=pr_FAOiA95ZI30AXifJGDUt_uid_unknown
  • https://asia.creativecdn.com/tags?id=pr_FAOiA95ZI30AXifJGDUt_offer_NUT-60023-01292-00001&id=pr_FAOiA95ZI30AXifJGDUt_uid_unknown&tc=1
0
0
206ms
206ms
Document
text/plain
103.132.192.30
RTB HOUSE PTE. LTD.
General
Full URL
https://asia.creativecdn.com/tags?id=pr_FAOiA95ZI30AXifJGDUt_offer_NUT-60023-01292-00001&id=pr_FAOiA95ZI30AXifJGDUt_uid_unknown&tc=1
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
103.132.192.30 , Singapore, ASN138552 (RTBHOUSE-AS-AP - RTB HOUSE PTE. LTD., SG),
Reverse DNS
ip-103-132-192-30.rtbhouse.net
Software
/
Resource Hash

Request headers

Referer
https://daftarslotterpercayaidn.com/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

Redirect headers

access-control-allow-credentials
true
access-control-allow-methods
GET, POST
access-control-allow-origin
*
access-control-max-age
3600
cache-control
no-cache, no-store, must-revalidate, private, max-age=0
content-length
0
date
Wed, 07 Oct 2026 05:00:09 GMT
expires
Thu, 01 Jan 1970 00:00:00 GMT Thu, 01 Jan 1970 00:00:00 GMT
location
https://asia.creativecdn.com/tags?id=pr_FAOiA95ZI30AXifJGDUt_offer_NUT-60023-01292-00001&id=pr_FAOiA95ZI30AXifJGDUt_uid_unknown&tc=1
p3p
CP="NON DSP COR CURa PSA PSD OUR BUS NAV STA"
pragma
no-cache
vary
Origin
GET
H2
404
925089264 Show response
td.doubleclick.net/td/rul/ Frame 9998
2 KB
2 KB
241ms
146ms
Document
text/html
142.251.14.157
Google LLC
General
Full URL
https://td.doubleclick.net/td/rul/925089264?random=1726498714047&cv=11&fst=1726498714047&fmt=3&bg=ffffff&guid=ON&async=1&gtm=45be4990z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1024&u_h=824&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=ecomm_pagetype%3Dproduct%3Becomm_prodid%3DNUT-60023-01292%3Becomm_totalvalue%3D343900
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.14.157 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f157.1e100.net
Software
/
Resource Hash
980ed2ca9a1e43c42e0d94a927fc79f3e07c62d0b9623501a2b8015d04948222

Request headers

Referer
https://daftarslotterpercayaidn.com/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
1577
content-type
text/html; charset=UTF-8
date
Wed, 07 Oct 2026 05:00:08 GMT
referrer-policy
no-referrer
GET
H2
404
920334631 Show response
td.doubleclick.net/td/rul/ Frame AA01
2 KB
2 KB
242ms
150ms
Document
text/html
142.251.14.157
Google LLC
General
Full URL
https://td.doubleclick.net/td/rul/920334631?random=1726498714059&cv=11&fst=1726498714059&fmt=3&bg=ffffff&guid=ON&async=1&gtm=45be4990z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1024&u_h=824&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=ecomm_pagetype%3Dretail-product-detail%3Becomm_prodid%3DNUT-60023-01292%3Becomm_totalvalue%3D343900
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
142.251.14.157 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
pm-in-f157.1e100.net
Software
/
Resource Hash
5f2badb55c07c25d970b453e5650df9ce4e86a6ca5b6f8a96f7041b73b9210ba

Request headers

Referer
https://daftarslotterpercayaidn.com/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
content-length
1577
content-type
text/html; charset=UTF-8
date
Wed, 07 Oct 2026 05:00:08 GMT
referrer-policy
no-referrer
GET
H2
200
events.js Show response
analytics.tiktok.com/i18n/pixel/
9 KB
3 KB
351ms
173ms
Script
application/javascript
92.123.104.175
AKAMAI-ASN1 Akama...
General
Full URL
https://analytics.tiktok.com/i18n/pixel/events.js?sdkid=C38OU43TAIRUEDS4L1L0&lib=ttq
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
92.123.104.175 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a92-123-104-175.deploy.static.akamaitechnologies.com
Software
nginx /
Resource Hash
7a7de1c15385fc9deab903e092b05599fc18558b914e80394cf7c1ea46b2fdf3

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-cache-remote
TCP_MISS from a23-48-200-171.deploy.akamaitechnologies.com (AkamaiGHost/22.6.4-888a2d21768272d5e2d80e9762941e76) (-)
expires
Wed, 07 Oct 2026 05:00:08 GMT
server-timing
cdn-cache; desc=MISS, edge; dur=89, origin; dur=8, inner; dur=2
x-cache
TCP_MISS from a23-67-40-56.deploy.akamaitechnologies.com (AkamaiGHost/22.6.4-888a2d21768272d5e2d80e9762941e76) (-)
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
x-akamai-request-id
47420bf3.a805f28
x-tt-trace-host
0165538117549bae1741fafe83dbf425740d63b9229b953d9623bc9c46304778ddfcf64ae4ac6a404b6d2eba55ee13bf213f7a52fad08d04e228e1a15081eea110425a59c420742b13ff5ee90a9c87d1bf5f35f8d6b8e638497e51ba04d05adec62a9d8ff02e0777ff6e0853ad6dc7d353effded10272671ea009733b3b79eb772a5e743858acae4136c20a681eca8798f
x-origin-response-time
8,23.48.200.171
cache-control
max-age=0, no-cache, no-store
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-tt-trace-tag
id=16;cdn-cache=miss;type=dyn
x-tt-trace-id
00-261007050008D12F9C207EA231886156-3E565AE421189B5E-00
x-parent-response-time
97,23.67.40.56
x-tt-logid
20261007050008D12F9C207EA231886156
server
nginx
POST
H3
200
collect
www.google.com/ccm/
0
0
49ms
49ms
Fetch
text/plain
142.251.156.119
Google LLC
General
Full URL
https://www.google.com/ccm/collect?rcb=0&frm=0&apvc=1&ae=g&auid=677347693.1791349208&dt=RAKYATJP%3A%20Rahasia%20Jam%20Gacor%20Slot%20Biar%20Cepat%20Maxwin&en=page_view&dl=https%3A%2F%2Fdaftarslotterpercayaidn.com%2F&scrsrc=www.googletagmanager.com&rnd=1416088682.1791349208&navt=n&npa=1&ep.ads_data_redaction=0&gtm=45He6a51v810058345za200zd810058345xeaxf1&gcd=13l3l3l2l1l1&dma_cps=a&dma=1&tag_exp=115616986~115938466~115938469~118897920~118897930~120385422~120469145~120469153~121046263~121046271~121246027~121246035~121280969~121427141&tft=1791349208458&tfd=2115&fmt=8
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtm.js?id=GTM-TKQZL95
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.156.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
/
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

POST
H3
204
collect
ad.doubleclick.net/ccm/s/
0
0
115ms
57ms
Fetch
text/html
142.251.127.149
Google LLC
General
Full URL
https://ad.doubleclick.net/ccm/s/collect?auid=677347693.1791349208&gtm=45He6a51v810058345za200zd810058345xeaxf1&fmt=8
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtm.js?id=GTM-TKQZL95
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.127.149 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfrai-in-f149.1e100.net
Software
/
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

GET
H3
200
daftarslotterpercayaidn.com.json Show response
script.crazyegg.com/pages/data-scripts/0075/7082/site/
12 KB
3 KB
91ms
60ms
XHR
application/json
104.19.147.8
Cloudflare
General
Full URL
https://script.crazyegg.com/pages/data-scripts/0075/7082/site/daftarslotterpercayaidn.com.json?t=1
Requested by
Host: script.crazyegg.com
URL: https://script.crazyegg.com/pages/scripts/0075/7082.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.19.147.8 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
408b20965467395fee579a2f356e3f37d3a2bb00078d3af0174f46aae1b52548

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

access-control-expose-headers
CE-Version
content-encoding
gzip
cf-cache-status
HIT
server-timing
cfExtPri
alt-svc
h3=":443"; ma=86400
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
application/json
last-modified
Wed, 07 Oct 2026 04:59:09 GMT
vary
accept-encoding
priority
u=1,i
cache-control
public, max-age=300, s-maxage=1209600
timing-allow-origin
*
cf-ray
a46a572989203eae-WAW
accept-ranges
bytes
access-control-allow-origin
*
content-length
2715
ce-version
11.5.557
server
cloudflare
GET
H3
200
1060020737679640 Show response
connect.facebook.net/signals/config/
515 KB
145 KB
272ms
272ms
Script
application/x-javascript
57.144.244.128
Facebook
General
Full URL
https://connect.facebook.net/signals/config/1060020737679640?v=2.9.414&r=stable&domain=daftarslotterpercayaidn.com&hme=a4c28c8787325ac3f8f9eac68364f47df2a8c4266e43177443e5d7f6289c9774&ex_m=117%2C240%2C170%2C27%2C81%2C82%2C161%2C77%2C76%2C11%2C180%2C101%2C20%2C152%2C140%2C46%2C84%2C89%2C148%2C175%2C182%2C8%2C4%2C5%2C7%2C6%2C3%2C102%2C114%2C32%2C17%2C31%2C18%2C33%2C34%2C35%2C37%2C55%2C162%2C86%2C125%2C22%2C24%2C51%2C47%2C49%2C48%2C94%2C103%2C107%2C123%2C159%2C163%2C53%2C124%2C29%2C26%2C132%2C78%2C43%2C165%2C164%2C166%2C156%2C154%2C30%2C42%2C66%2C122%2C177%2C79%2C21%2C127%2C92%2C75%2C23%2C96%2C97%2C129%2C95%2C150%2C149%2C153%2C108%2C176%2C179%2C41%2C56%2C126%2C54%2C160%2C71%2C184%2C109%2C183%2C209%2C254%2C83%2C273%2C272%2C271%2C14%2C25%2C28%2C40%2C62%2C116%2C68%2C10%2C72%2C110%2C111%2C112%2C118%2C143%2C38%2C36%2C145%2C146%2C147%2C142%2C141%2C171%2C85%2C174%2C172%2C173%2C57%2C67%2C136%2C19%2C178%2C52%2C322%2C323%2C324%2C321%2C337%2C359%2C247%2C236%2C69%2C237%2C235%2C362%2C353%2C59%2C248%2C120%2C144%2C91%2C134%2C61%2C133%2C139%2C138%2C65%2C73%2C167%2C87%2C88%2C128%2C44%2C39%2C60%2C63%2C113%2C181%2C1%2C137%2C16%2C135%2C12%2C2%2C64%2C104%2C15%2C74%2C70%2C131%2C100%2C99%2C186%2C187%2C105%2C106%2C9%2C115%2C185%2C58%2C157%2C98%2C90%2C80%2C130%2C119%2C168%2C50%2C158%2C0%2C93%2C151%2C155%2C169%2C45%2C121%2C13%2C188
Requested by
Host: connect.facebook.net
URL: https://connect.facebook.net/en_US/fbevents.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
57.144.244.128 Frankfurt am Main, Germany, ASN32934 (FACEBOOK - Facebook, Inc., US),
Reverse DNS
xx-fbcdn-shv-01-fra5.fbcdn.net
Software
/
Resource Hash
566134ecec9a65a92f3b48b95e8227974a09fefa7a985a57d58f731da5249f99
Security Headers
Name Value
Content-Security-Policy default-src *.facebook.com *.fbcdn.net *.facebook.net 'self' blob:;script-src *.facebook.com *.fbcdn.net *.facebook.net blob: 'self' 'nonce-OBov0sx5';style-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob: 'unsafe-inline';connect-src *.facebook.com facebook.com *.fbcdn.net *.facebook.net wss://*.facebook.com:* wss://*.fbcdn.net attachment.fbsbx.com *.cdninstagram.com blob: 'self' data: https://edge-chat.facebook.net https://edge-chat-latest.facebook.net wss://edge-chat-latest.facebook.net wss://edge-chat.facebook.net wss://edge-chat.socialplugin.facebook.net wss://edge-chat-latest.socialplugin.facebook.net https://edge-chat.socialplugin.facebook.net https://edge-chat-latest.socialplugin.facebook.net;font-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;img-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;media-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;child-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;frame-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;manifest-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;object-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;worker-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;block-all-mixed-content;upgrade-insecure-requests;report-uri https://www.facebook.com/csp/reporting/?m=c&minimize=0;
Strict-Transport-Security max-age=31536000; preload; includeSubDomains
X-Content-Type-Options nosniff
X-Frame-Options DENY
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
report-to
{"max_age":2592000,"endpoints":[{"url":"https:\/\/www.facebook.com\/browser_reporting\/coop\/?minimize=0"}],"group":"coop_report","include_subdomains":true}, {"max_age":86400,"endpoints":[{"url":"https:\/\/www.facebook.com\/browser_reporting\/coep\/?minimize=0"}],"group":"coep_report"}, {"max_age":21600,"endpoints":[{"url":"https:\/\/www.facebook.com\/ajax\/browser_error_reports\/"}],"group":"permissions_policy"}
x-content-type-options
nosniff
expires
Sat, 01 Jan 2000 00:00:00 GMT
alt-svc
h3=":443"; ma=86400
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
application/x-javascript; charset=utf-8
vary
Accept-Encoding
cross-origin-embedder-policy-report-only
require-corp;report-to="coep_report"
priority
u=3,i
x-frame-options
DENY
strict-transport-security
max-age=31536000; preload; includeSubDomains
reporting-endpoints
coop_report="https://www.facebook.com/browser_reporting/coop/?minimize=0", coep_report="https://www.facebook.com/browser_reporting/coep/?minimize=0", permissions_policy="https://www.facebook.com/ajax/browser_error_reports/"
content-security-policy
default-src *.facebook.com *.fbcdn.net *.facebook.net 'self' blob:;script-src *.facebook.com *.fbcdn.net *.facebook.net blob: 'self' 'nonce-OBov0sx5';style-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob: 'unsafe-inline';connect-src *.facebook.com facebook.com *.fbcdn.net *.facebook.net wss://*.facebook.com:* wss://*.fbcdn.net attachment.fbsbx.com *.cdninstagram.com blob: 'self' data: https://edge-chat.facebook.net https://edge-chat-latest.facebook.net wss://edge-chat-latest.facebook.net wss://edge-chat.facebook.net wss://edge-chat.socialplugin.facebook.net wss://edge-chat-latest.socialplugin.facebook.net https://edge-chat.socialplugin.facebook.net https://edge-chat-latest.socialplugin.facebook.net;font-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;img-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;media-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;child-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;frame-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;manifest-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;object-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;worker-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;block-all-mixed-content;upgrade-insecure-requests;report-uri https://www.facebook.com/csp/reporting/?m=c&minimize=0;
cache-control
public, max-age=1200
timing-allow-origin
*
cross-origin-opener-policy
same-origin-allow-popups
x-fb-connection-quality
EXCELLENT; q=0.9, rtt=48, rtx=0, c=131, mss=1232, tbw=228391, tp=202, tpl=0, uplat=221, ullat=0
pragma
public
x-fb-debug
GCGPYjpfd9UjlNtsEGaXaq8Y5Jdsvoeux75oq3Fw1j6fWpS23fu5sGwua0v/wdtiFesA/2zSeyBs7zfsiK4zOQ==
cross-origin-resource-policy
cross-origin
permissions-policy
accelerometer=(), attribution-reporting=(), autoplay=(), bluetooth=(), camera=(), ch-device-memory=(), ch-downlink=(), ch-dpr=(), ch-ect=(), ch-rtt=(), ch-save-data=(), ch-ua-arch=(), ch-ua-bitness=(), ch-viewport-height=(), ch-viewport-width=(), ch-width=(), clipboard-read=(), clipboard-write=(), compute-pressure=(), display-capture=(), encrypted-media=(), fullscreen=(self), gamepad=(), geolocation=(), gyroscope=(), hid=(), idle-detection=(), interest-cohort=(), keyboard-map=(), local-fonts=(), magnetometer=(), microphone=(), midi=(), otp-credentials=(), payment=(), picture-in-picture=(), private-state-token-issuance=(), publickey-credentials-get=(), screen-wake-lock=(), serial=(), shared-storage=(), shared-storage-select-url=(), private-state-token-redemption=(), usb=(), unload=(self), window-management=(), xr-spatial-tracking=();report-to="permissions_policy"
document-policy
force-load-at-top, include-js-call-stacks-in-crash-reports
x-xss-protection
0
origin-agent-cluster
?1
GET
H2
200
adsct
t.co/1/i/
43 B
134 B
177ms
176ms
Image
image/gif
172.66.0.227
Cloudflare
General
Full URL
https://t.co/1/i/adsct?bci=4&dv=Europe%2FWarsaw%26pl-PL%26Google%20Inc.%26Linux%20x86_64%26255%261600%261200%2630%2624%261600%261200%260%26na&eci=3&event=%7B%7D&event_id=8189cfa8-85e3-4958-8072-7fc75db79d30&integration=advertiser&p_id=Twitter&p_user_id=0&pl_id=dfeffaca-63cf-4712-8a58-902da860285f&tw_ch_fvl=Chromium%2F154.0.8037.97%2CGoogle%20Chrome%2F154.0.8037.97%2CNot%20A(Brand%2F99.0.0.0&tw_document_href=https%3A%2F%2Fdaftarslotterpercayaidn.com%2F&tw_engaged_ms=1&tw_iframe_status=0&tw_pid_src=1&tw_session_count=1&tw_session_id=1791349208575-286052253&tw_session_start=1&twpid=tw.1791349208575.807347861613528788&txn_id=nvqtr&type=javascript&version=2.4.11
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.66.0.227 , United States, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare envoy /
Resource Hash
ac8778041fdb7f2e08ceb574c9a766247ea26f1a7d90fa854c4efcf4b361a957
Security Headers
Name Value
Strict-Transport-Security max-age=631138519; includeSubdomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=631138519; includeSubdomains
x-transaction-id
ac1e23ea736050f4
cache-control
no-cache, no-store, max-age=0
origin-cf-ray
a46a5729ca2f6338-WAW
cf-cache-status
DYNAMIC
cf-ray
a46a5729ca2f6338-WAW
x-response-time
7
content-length
43
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
image/gif;charset=utf-8
perf
7402827104
server
cloudflare envoy
x-served-by
t4_a
GET
H2
200
adsct
analytics.twitter.com/1/i/
43 B
203 B
159ms
158ms
Image
image/gif
172.66.0.227
Cloudflare
General
Full URL
https://analytics.twitter.com/1/i/adsct?bci=4&dv=Europe%2FWarsaw%26pl-PL%26Google%20Inc.%26Linux%20x86_64%26255%261600%261200%2630%2624%261600%261200%260%26na&eci=3&event=%7B%7D&event_id=8189cfa8-85e3-4958-8072-7fc75db79d30&integration=advertiser&p_id=Twitter&p_user_id=0&pl_id=dfeffaca-63cf-4712-8a58-902da860285f&tw_ch_fvl=Chromium%2F154.0.8037.97%2CGoogle%20Chrome%2F154.0.8037.97%2CNot%20A(Brand%2F99.0.0.0&tw_document_href=https%3A%2F%2Fdaftarslotterpercayaidn.com%2F&tw_engaged_ms=1&tw_iframe_status=0&tw_pid_src=1&tw_session_count=1&tw_session_id=1791349208575-286052253&tw_session_start=1&twpid=tw.1791349208575.807347861613528788&txn_id=nvqtr&type=javascript&version=2.4.11
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
172.66.0.227 , United States, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare envoy /
Resource Hash
ac8778041fdb7f2e08ceb574c9a766247ea26f1a7d90fa854c4efcf4b361a957
Security Headers
Name Value
Strict-Transport-Security max-age=631138519; includeSubdomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=631138519; includeSubdomains
x-transaction-id
d7711035251b22c3
cache-control
no-cache, no-store, max-age=0
origin-cf-ray
a46a5729c8881607-WAW
cf-cache-status
DYNAMIC
cf-ray
a46a5729c8881607-WAW
x-response-time
7
content-length
43
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
image/gif;charset=utf-8
perf
7402827104
server
cloudflare envoy
x-served-by
t4_a
GET
H3
200
0890f4eaeb0cb04f734921762ba0d327.js Show response
script.crazyegg.com/pages/versioned/common-scripts/
200 KB
64 KB
35ms
35ms
Script
text/javascript
104.19.147.8
Cloudflare
General
Full URL
https://script.crazyegg.com/pages/versioned/common-scripts/0890f4eaeb0cb04f734921762ba0d327.js
Requested by
Host: script.crazyegg.com
URL: https://script.crazyegg.com/pages/scripts/0075/7082.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.19.147.8 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
d3e7edc241acef61b4e3d9169d95bbecd423c250fde643b663b661b52d3cc3e3

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
cf-cache-status
HIT
age
116695
server-timing
cfExtPri
alt-svc
h3=":443"; ma=86400
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
text/javascript
last-modified
Mon, 05 Oct 2026 20:24:24 GMT
vary
accept-encoding
priority
u=3,i=?0
cache-control
public, max-age=31536000, s-maxage=31536000
timing-allow-origin
*
cf-ray
a46a5729e8b2bf47-WAW
accept-ranges
bytes
access-control-allow-origin
*
content-length
65463
server
cloudflare
GET
H3
200
googlelogo_color_150x54dp.png
www.google.com/images/branding/googlelogo/1x/ Frame 75DE
3 KB
3 KB
100ms
51ms
Image
image/png
142.251.157.119
Google LLC
General
Full URL
https://www.google.com/images/branding/googlelogo/1x/googlelogo_color_150x54dp.png
Requested by
Host: td.doubleclick.net
URL: https://td.doubleclick.net/td/rul/880395410?random=1726498671571&cv=11&fst=1726498671571&fmt=3&bg=ffffff&guid=ON&async=1&gtm=45je4990v877689920z8810058345za200zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FmetaData%3D4eHyfurj4yL7Q4Ucv84uGYHJb0g2t%2BFdwECMb3QsHNjtAqmaWkaBfGgt5w9qTEikAP03CsR8aLRQodyhRwzA9w%3D%3D%26pickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Online%20Mall%20Blibli.com%2C%20Sensasi%20Belanja%20Online%20Shop%20ala%20Mall&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=event%3Dgtag.config
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.157.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
dbef5e5530003b7233e944856c23d1437902a2d3568cdfd2beaf2166e9ca9139
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://td.doubleclick.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
private, max-age=31536000
cross-origin-resource-policy
cross-origin
report-to
{"group":"static-on-bigtable","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/static-on-bigtable"}]}
x-content-type-options
nosniff
expires
Wed, 07 Oct 2026 05:00:08 GMT
accept-ranges
bytes
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cross-origin-opener-policy-report-only
same-origin; report-to="static-on-bigtable"
content-length
3170
date
Wed, 07 Oct 2026 05:00:08 GMT
x-xss-protection
0
content-type
image/png
last-modified
Tue, 22 Oct 2019 18:30:00 GMT
server
sffe
GET
H2
200
ins.js Show response
blibli.api.useinsider.com/
0
50 B
38ms
38ms
Script
application/javascript
162.159.133.61
Cloudflare
General
Full URL
https://blibli.api.useinsider.com/ins.js?id=10001129
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
162.159.133.61 , United States, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Content-Type-Options nosniff
X-Frame-Options SAMEORIGIN
X-Xss-Protection 1

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cf-cache-status
HIT
x-amz-version-id
PxtiBxtLSjQmNUlRe.SB2GLWi5wUB_ti
age
828
etag
"d41d8cd98f00b204e9800998ecf8427e"
x-content-type-options
nosniff
expires
Wed, 07 Oct 2026 05:05:08 GMT
date
Wed, 07 Oct 2026 05:00:08 GMT
last-modified
Thu, 14 Mar 2024 08:46:20 GMT
vary
accept-encoding
content-type
application/javascript; charset=UTF-8
x-amz-id-2
Mz5gRCyJhhwCfTNitpAOQBc3dF+MiJGzt76Rt4uOa872BawdwNDPzrSvrr1IFZIjCw+V14Siedo=
x-frame-options
SAMEORIGIN
strict-transport-security
max-age=31536000; includeSubDomains
cache-control
public, max-age=300
pragma
public
x-amz-request-id
62J24473CQ7F609E
cf-ray
a46a572a0f04f59c-WAW
accept-ranges
bytes
access-control-allow-origin
*
content-length
0
x-xss-protection
1
server
cloudflare
GET
H3
200
googlelogo_color_150x54dp.png
www.google.com/images/branding/googlelogo/1x/ Frame A779
3 KB
0
92ms
92ms
Image
image/png
142.251.157.119
Google LLC
General
Full URL
https://www.google.com/images/branding/googlelogo/1x/googlelogo_color_150x54dp.png
Requested by
Host: td.doubleclick.net
URL: https://td.doubleclick.net/td/rul/920334631?random=1726498673536&cv=11&fst=1726498673536&fmt=3&bg=ffffff&guid=ON&async=1&gtm=45be4990z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=ecomm_pagetype%3Dretail-product-detail%3Becomm_prodid%3DNUT-60023-01292%3Becomm_totalvalue%3D343900
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.157.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
dbef5e5530003b7233e944856c23d1437902a2d3568cdfd2beaf2166e9ca9139
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://td.doubleclick.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
private, max-age=31536000
cross-origin-resource-policy
cross-origin
report-to
{"group":"static-on-bigtable","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/static-on-bigtable"}]}
x-content-type-options
nosniff
expires
Wed, 07 Oct 2026 05:00:08 GMT
accept-ranges
bytes
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cross-origin-opener-policy-report-only
same-origin; report-to="static-on-bigtable"
content-length
3170
date
Wed, 07 Oct 2026 05:00:08 GMT
x-xss-protection
0
content-type
image/png
last-modified
Tue, 22 Oct 2019 18:30:00 GMT
server
sffe
GET
H3
200
googlelogo_color_150x54dp.png
www.google.com/images/branding/googlelogo/1x/ Frame B6F7
3 KB
0
92ms
92ms
Image
image/png
142.251.157.119
Google LLC
General
Full URL
https://www.google.com/images/branding/googlelogo/1x/googlelogo_color_150x54dp.png
Requested by
Host: td.doubleclick.net
URL: https://td.doubleclick.net/td/rul/880395410?random=1726498673589&cv=11&fst=1726498673589&fmt=3&bg=ffffff&guid=ON&async=1&gtm=45be4990v877689920z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&label=hEx3CKjo-eADEJKJ56MD&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&value=0&bttype=purchase&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&capi=1&ct_cookie_present=0
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.157.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
dbef5e5530003b7233e944856c23d1437902a2d3568cdfd2beaf2166e9ca9139
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://td.doubleclick.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
private, max-age=31536000
cross-origin-resource-policy
cross-origin
report-to
{"group":"static-on-bigtable","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/static-on-bigtable"}]}
x-content-type-options
nosniff
expires
Wed, 07 Oct 2026 05:00:08 GMT
accept-ranges
bytes
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cross-origin-opener-policy-report-only
same-origin; report-to="static-on-bigtable"
content-length
3170
date
Wed, 07 Oct 2026 05:00:08 GMT
x-xss-protection
0
content-type
image/png
last-modified
Tue, 22 Oct 2019 18:30:00 GMT
server
sffe
GET
H3
200
googlelogo_color_150x54dp.png
www.google.com/images/branding/googlelogo/1x/ Frame 9998
3 KB
0
92ms
92ms
Image
image/png
142.251.157.119
Google LLC
General
Full URL
https://www.google.com/images/branding/googlelogo/1x/googlelogo_color_150x54dp.png
Requested by
Host: td.doubleclick.net
URL: https://td.doubleclick.net/td/rul/925089264?random=1726498714047&cv=11&fst=1726498714047&fmt=3&bg=ffffff&guid=ON&async=1&gtm=45be4990z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1024&u_h=824&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=ecomm_pagetype%3Dproduct%3Becomm_prodid%3DNUT-60023-01292%3Becomm_totalvalue%3D343900
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.157.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
dbef5e5530003b7233e944856c23d1437902a2d3568cdfd2beaf2166e9ca9139
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://td.doubleclick.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
private, max-age=31536000
cross-origin-resource-policy
cross-origin
report-to
{"group":"static-on-bigtable","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/static-on-bigtable"}]}
x-content-type-options
nosniff
expires
Wed, 07 Oct 2026 05:00:08 GMT
accept-ranges
bytes
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cross-origin-opener-policy-report-only
same-origin; report-to="static-on-bigtable"
content-length
3170
date
Wed, 07 Oct 2026 05:00:08 GMT
x-xss-protection
0
content-type
image/png
last-modified
Tue, 22 Oct 2019 18:30:00 GMT
server
sffe
GET
H3
200
googlelogo_color_150x54dp.png
www.google.com/images/branding/googlelogo/1x/ Frame AA01
3 KB
0
87ms
87ms
Image
image/png
142.251.157.119
Google LLC
General
Full URL
https://www.google.com/images/branding/googlelogo/1x/googlelogo_color_150x54dp.png
Requested by
Host: td.doubleclick.net
URL: https://td.doubleclick.net/td/rul/920334631?random=1726498714059&cv=11&fst=1726498714059&fmt=3&bg=ffffff&guid=ON&async=1&gtm=45be4990z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1024&u_h=824&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=ecomm_pagetype%3Dretail-product-detail%3Becomm_prodid%3DNUT-60023-01292%3Becomm_totalvalue%3D343900
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.157.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
dbef5e5530003b7233e944856c23d1437902a2d3568cdfd2beaf2166e9ca9139
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://td.doubleclick.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
private, max-age=31536000
cross-origin-resource-policy
cross-origin
report-to
{"group":"static-on-bigtable","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/static-on-bigtable"}]}
x-content-type-options
nosniff
expires
Wed, 07 Oct 2026 05:00:08 GMT
accept-ranges
bytes
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cross-origin-opener-policy-report-only
same-origin; report-to="static-on-bigtable"
content-length
3170
date
Wed, 07 Oct 2026 05:00:08 GMT
x-xss-protection
0
content-type
image/png
last-modified
Tue, 22 Oct 2019 18:30:00 GMT
server
sffe
GET
H2
503
site
t.o-s.io/
19 B
19 B
180ms
59ms
Image
text/plain
35.244.195.172
Google LLC
General
Full URL
https://t.o-s.io/site?res=1600x1200&lang=pl&client_id=115069&product_category=default&item_identifier=%3CITEM%20ID%3E&_ur=41034427&_ref=
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
35.244.195.172 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
172.195.244.35.bc.googleusercontent.com
Software
/
Resource Hash
7ac9c58532de36879ea6d7d357f8878e16a18bff367f898fb7db398a9ae643c5

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

via
1.1 google
alt-svc
h3=":443"; ma=2592000
content-length
19
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
text/plain
GET
H3
200
googlelogo_color_150x54dp.png
www.google.com/images/branding/googlelogo/1x/ Frame 7923
3 KB
0
82ms
82ms
Image
image/png
142.251.157.119
Google LLC
General
Full URL
https://www.google.com/images/branding/googlelogo/1x/googlelogo_color_150x54dp.png
Requested by
Host: td.doubleclick.net
URL: https://td.doubleclick.net/td/rul/925089264?random=1726498673524&cv=11&fst=1726498673524&fmt=3&bg=ffffff&guid=ON&async=1&gtm=45be4990z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=ecomm_pagetype%3Dproduct%3Becomm_prodid%3DNUT-60023-01292%3Becomm_totalvalue%3D343900
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.157.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
sffe /
Resource Hash
dbef5e5530003b7233e944856c23d1437902a2d3568cdfd2beaf2166e9ca9139
Security Headers
Name Value
X-Content-Type-Options nosniff
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://td.doubleclick.net/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
private, max-age=31536000
cross-origin-resource-policy
cross-origin
report-to
{"group":"static-on-bigtable","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/static-on-bigtable"}]}
x-content-type-options
nosniff
expires
Wed, 07 Oct 2026 05:00:08 GMT
accept-ranges
bytes
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
cross-origin-opener-policy-report-only
same-origin; report-to="static-on-bigtable"
content-length
3170
date
Wed, 07 Oct 2026 05:00:08 GMT
x-xss-protection
0
content-type
image/png
last-modified
Tue, 22 Oct 2019 18:30:00 GMT
server
sffe
GET
H3
200
daftarslotterpercayaidn.com.json Show response
script.crazyegg.com/pages/data-scripts/0075/7082/sampling/
212 B
395 B
58ms
58ms
XHR
application/json
104.19.147.8
Cloudflare
General
Full URL
https://script.crazyegg.com/pages/data-scripts/0075/7082/sampling/daftarslotterpercayaidn.com.json?t=1
Requested by
Host: script.crazyegg.com
URL: https://script.crazyegg.com/pages/versioned/common-scripts/db7349b994413162218df5c920535415.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.19.147.8 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
e7368a0cfada6443baf2b3ae47db15ff08df634ea10b2bebd0a5c5fe8e37b3f0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

access-control-expose-headers
CE-Version
content-encoding
gzip
cf-cache-status
HIT
server-timing
cfExtPri
alt-svc
h3=":443"; ma=86400
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
application/json
last-modified
Wed, 07 Oct 2026 04:59:10 GMT
vary
accept-encoding
priority
u=1,i
cache-control
public, max-age=300, s-maxage=1209600
timing-allow-origin
*
cf-ray
a46a572a49343eae-WAW
accept-ranges
bytes
access-control-allow-origin
*
content-length
170
ce-version
11.5.557
server
cloudflare
GET
H2
200
t.json Show response
media.flixcar.com/modular/web-api/id/12612/749921021090NUT-60023-01292ZGFmdGFyc2xvdHRlcnBlcmNheWFpZG4uY29t/
18 B
345 B
52ms
51ms
Fetch
application/json
18.64.211.128
Amazon.com
General
Full URL
https://media.flixcar.com/modular/web-api/id/12612/749921021090NUT-60023-01292ZGFmdGFyc2xvdHRlcnBlcmNheWFpZG4uY29t/t.json?mpn=749921021090&ean=NUT-60023-01292&distId=12612&iso=id&flIso=e2
Requested by
Host: media.flixcar.com
URL: https://media.flixcar.com/modular/js/minify/12612/?url=/clamps/modularvnew/js/service.js&v=32&ftype=inpage&d=12612&l=id&mpn=749921021090&ean=NUT-60023-01292&brand=Tropicana%20Slim&fl=e2&ssl=1&dmn=ZGFmdGFyc2xvdHRlcnBlcmNheWFpZG4uY29t&ext=.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
18.64.211.128 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-18-64-211-128.fra56.r.cloudfront.net
Software
CloudFront /
Resource Hash
7992b83823c161d3447d6fc3aaa10be33267de183d2d1120e7301720fc8b0ce0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
public, max-age=86400, s-maxage=86400, immutable
age
60
via
1.1 8d71893c94b38234ca2b7efa272a14b8.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Hit from cloudfront
content-length
18
x-amz-cf-id
YJIX_AZifLvHyjHxtYNomJL77q1fZoo_dqro25V2vXyV5dcfFiuGiw==
date
Wed, 07 Oct 2026 04:59:08 GMT
content-type
application/json;charset=utf-8
x-amz-cf-pop
FRA56-P16
server
CloudFront
GET
H2
200
main.MWU2MzIzODM0MQ.js Show response
analytics.tiktok.com/i18n/pixel/static/
485 KB
115 KB
56ms
56ms
Script
application/javascript
92.123.104.175
AKAMAI-ASN1 Akama...
General
Full URL
https://analytics.tiktok.com/i18n/pixel/static/main.MWU2MzIzODM0MQ.js
Requested by
Host: analytics.tiktok.com
URL: https://analytics.tiktok.com/i18n/pixel/events.js?sdkid=C38OU43TAIRUEDS4L1L0&lib=ttq
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
92.123.104.175 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a92-123-104-175.deploy.static.akamaitechnologies.com
Software
nginx /
Resource Hash
aab6a662df923c04739f37c6a6d7f13fb91c8e3c6addd82fd5a6959e6f6241fb

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

x-cache
TCP_HIT from a23-67-40-56.deploy.akamaitechnologies.com (AkamaiGHost/22.6.4-888a2d21768272d5e2d80e9762941e76) (-)
vary
Accept-Encoding
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
cross-origin-resource-policy
cross-origin
x-tt-trace-tag
id=16;cdn-cache=hit;type=static
server-timing
cdn-cache; desc=HIT, edge; dur=0, origin; dur=0, inner; dur=44
x-tt-trace-id
00-260918075752BA0534280C42755133DB-649DC33E5F0DFBA6-00
content-length
117050
date
Wed, 07 Oct 2026 05:00:08 GMT
content-type
application/javascript; charset=UTF-8
x-tt-logid
20260918075752BA0534280C42755133DB
server
nginx
x-akamai-request-id
a805f55
x-tt-trace-host
01029be0daea8c3c786dcf71026acff931e915ace5342918c77f5e0525e6fd2d747414a6aff988b4d31773aba190e64a6472797a6fb83794bfb3eb7b58d2f9f0ac7569d7f303bb6179bfc2da5fdf6bd7eb6e93cfad13b6a3d827fbcb37261c6fc7
POST
H2
200
events
dv-c3e594c6d429469e90b54478358619c3.ecs.us-east-1.on.aws/
0
0
569ms
249ms
Fetch
application/json
34.193.159.151
Amazon.com
General
Full URL
https://dv-c3e594c6d429469e90b54478358619c3.ecs.us-east-1.on.aws/events?cee=no
Requested by
Host: connect.facebook.net
URL: https://connect.facebook.net/signals/config/1060020737679640?v=2.9.414&r=stable&domain=daftarslotterpercayaidn.com&hme=a4c28c8787325ac3f8f9eac68364f47df2a8c4266e43177443e5d7f6289c9774&ex_m=117%2C240%2C170%2C27%2C81%2C82%2C161%2C77%2C76%2C11%2C180%2C101%2C20%2C152%2C140%2C46%2C84%2C89%2C148%2C175%2C182%2C8%2C4%2C5%2C7%2C6%2C3%2C102%2C114%2C32%2C17%2C31%2C18%2C33%2C34%2C35%2C37%2C55%2C162%2C86%2C125%2C22%2C24%2C51%2C47%2C49%2C48%2C94%2C103%2C107%2C123%2C159%2C163%2C53%2C124%2C29%2C26%2C132%2C78%2C43%2C165%2C164%2C166%2C156%2C154%2C30%2C42%2C66%2C122%2C177%2C79%2C21%2C127%2C92%2C75%2C23%2C96%2C97%2C129%2C95%2C150%2C149%2C153%2C108%2C176%2C179%2C41%2C56%2C126%2C54%2C160%2C71%2C184%2C109%2C183%2C209%2C254%2C83%2C273%2C272%2C271%2C14%2C25%2C28%2C40%2C62%2C116%2C68%2C10%2C72%2C110%2C111%2C112%2C118%2C143%2C38%2C36%2C145%2C146%2C147%2C142%2C141%2C171%2C85%2C174%2C172%2C173%2C57%2C67%2C136%2C19%2C178%2C52%2C322%2C323%2C324%2C321%2C337%2C359%2C247%2C236%2C69%2C237%2C235%2C362%2C353%2C59%2C248%2C120%2C144%2C91%2C134%2C61%2C133%2C139%2C138%2C65%2C73%2C167%2C87%2C88%2C128%2C44%2C39%2C60%2C63%2C113%2C181%2C1%2C137%2C16%2C135%2C12%2C2%2C64%2C104%2C15%2C74%2C70%2C131%2C100%2C99%2C186%2C187%2C105%2C106%2C9%2C115%2C185%2C58%2C157%2C98%2C90%2C80%2C130%2C119%2C168%2C50%2C158%2C0%2C93%2C151%2C155%2C169%2C45%2C121%2C13%2C188
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
34.193.159.151 Ashburn, United States, ASN14618 (AMAZON-AES - Amazon.com, Inc., US),
Reverse DNS
ec2-34-193-159-151.compute-1.amazonaws.com
Software
/
Resource Hash
Security Headers
Name Value
Content-Security-Policy default-src 'none'
Strict-Transport-Security max-age=31536000
X-Content-Type-Options nosniff

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

strict-transport-security
max-age=31536000
content-security-policy
default-src 'none'
access-control-allow-credentials
true
x-content-type-options
nosniff
access-control-allow-origin
https://daftarslotterpercayaidn.com
content-length
0
date
Wed, 07 Oct 2026 05:00:09 GMT
content-type
application/json
vary
origin
GET
H3
200
515463815273206 Show response
connect.facebook.net/signals/config/
25 KB
7 KB
485ms
485ms
Script
application/x-javascript
57.144.244.128
Facebook
General
Full URL
https://connect.facebook.net/signals/config/515463815273206?v=2.9.414&r=stable&domain=daftarslotterpercayaidn.com&hme=a4c28c8787325ac3f8f9eac68364f47df2a8c4266e43177443e5d7f6289c9774&ex_m=117%2C240%2C170%2C27%2C81%2C82%2C161%2C77%2C76%2C11%2C180%2C101%2C20%2C152%2C140%2C46%2C84%2C89%2C148%2C175%2C182%2C8%2C4%2C5%2C7%2C6%2C3%2C102%2C114%2C32%2C17%2C31%2C18%2C33%2C34%2C35%2C37%2C55%2C162%2C86%2C125%2C22%2C24%2C51%2C47%2C49%2C48%2C94%2C103%2C107%2C123%2C159%2C163%2C53%2C124%2C29%2C26%2C132%2C78%2C43%2C165%2C164%2C166%2C156%2C154%2C30%2C42%2C66%2C122%2C177%2C79%2C21%2C127%2C92%2C75%2C23%2C96%2C97%2C129%2C95%2C150%2C149%2C153%2C108%2C176%2C179%2C41%2C56%2C126%2C54%2C160%2C71%2C184%2C109%2C183%2C209%2C254%2C83%2C273%2C272%2C271%2C14%2C25%2C28%2C40%2C62%2C116%2C68%2C10%2C72%2C110%2C111%2C112%2C118%2C143%2C38%2C36%2C145%2C146%2C147%2C142%2C141%2C171%2C85%2C174%2C172%2C173%2C57%2C67%2C136%2C19%2C178%2C52%2C322%2C323%2C324%2C321%2C337%2C359%2C247%2C236%2C69%2C237%2C235%2C362%2C353%2C59%2C248%2C120%2C144%2C91%2C134%2C61%2C133%2C139%2C138%2C65%2C73%2C167%2C87%2C88%2C128%2C44%2C39%2C60%2C63%2C113%2C181%2C1%2C137%2C16%2C135%2C12%2C2%2C64%2C104%2C15%2C74%2C70%2C131%2C100%2C99%2C186%2C187%2C105%2C106%2C9%2C115%2C185%2C58%2C157%2C98%2C90%2C80%2C130%2C119%2C168%2C50%2C158%2C0%2C93%2C151%2C155%2C169%2C45%2C121%2C13%2C188%2C267%2C265%2C260%2C262%2C263%2C264%2C261%2C259%2C246%2C266%2C268%2C258%2C216%2C217%2C269%2C270%2C257%2C256%2C351%2C352%2C229%2C224%2C227%2C228%2C206%2C222%2C387%2C303%2C307%2C310%2C311%2C312%2C308%2C313%2C306%2C301%2C315%2C316%2C305%2C314%2C318%2C309%2C304%2C317%2C319%2C302%2C239%2C300%2C205%2C225%2C226%2C250%2C223%2C221%2C277%2C241%2C214%2C215%2C211%2C212%2C213%2C210%2C208%2C219%2C220%2C218%2C325%2C380%2C345%2C346%2C348%2C349%2C347%2C344%2C343%2C230%2C280%2C287%2C288%2C281%2C283%2C286%2C284%2C285%2C282%2C279%2C298%2C292%2C295%2C291%2C299%2C296%2C290%2C294%2C297%2C293%2C289%2C339%2C356
Requested by
Host: connect.facebook.net
URL: https://connect.facebook.net/en_US/fbevents.js
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
57.144.244.128 Frankfurt am Main, Germany, ASN32934 (FACEBOOK - Facebook, Inc., US),
Reverse DNS
xx-fbcdn-shv-01-fra5.fbcdn.net
Software
/
Resource Hash
cca7772f89154d90db384f90e3ea0cfa81ea4b891fa3ba6da177f8d43349b01a
Security Headers
Name Value
Content-Security-Policy default-src *.facebook.com *.fbcdn.net *.facebook.net 'self' blob:;script-src *.facebook.com *.fbcdn.net *.facebook.net blob: 'self' 'nonce-gzcsO44b';style-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob: 'unsafe-inline';connect-src *.facebook.com facebook.com *.fbcdn.net *.facebook.net wss://*.facebook.com:* wss://*.fbcdn.net attachment.fbsbx.com *.cdninstagram.com blob: 'self' data: https://edge-chat.facebook.net https://edge-chat-latest.facebook.net wss://edge-chat-latest.facebook.net wss://edge-chat.facebook.net wss://edge-chat.socialplugin.facebook.net wss://edge-chat-latest.socialplugin.facebook.net https://edge-chat.socialplugin.facebook.net https://edge-chat-latest.socialplugin.facebook.net;font-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;img-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;media-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;child-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;frame-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;manifest-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;object-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;worker-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;block-all-mixed-content;upgrade-insecure-requests;report-uri https://www.facebook.com/csp/reporting/?m=c&minimize=0;
Strict-Transport-Security max-age=31536000; preload; includeSubDomains
X-Content-Type-Options nosniff
X-Frame-Options DENY
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
report-to
{"max_age":2592000,"endpoints":[{"url":"https:\/\/www.facebook.com\/browser_reporting\/coop\/?minimize=0"}],"group":"coop_report","include_subdomains":true}, {"max_age":86400,"endpoints":[{"url":"https:\/\/www.facebook.com\/browser_reporting\/coep\/?minimize=0"}],"group":"coep_report"}, {"max_age":21600,"endpoints":[{"url":"https:\/\/www.facebook.com\/ajax\/browser_error_reports\/"}],"group":"permissions_policy"}
x-content-type-options
nosniff
expires
Sat, 01 Jan 2000 00:00:00 GMT
alt-svc
h3=":443"; ma=86400
date
Wed, 07 Oct 2026 05:00:09 GMT
content-type
application/x-javascript; charset=utf-8
vary
Accept-Encoding
cross-origin-embedder-policy-report-only
require-corp;report-to="coep_report"
priority
u=3,i
x-frame-options
DENY
strict-transport-security
max-age=31536000; preload; includeSubDomains
reporting-endpoints
coop_report="https://www.facebook.com/browser_reporting/coop/?minimize=0", coep_report="https://www.facebook.com/browser_reporting/coep/?minimize=0", permissions_policy="https://www.facebook.com/ajax/browser_error_reports/"
content-security-policy
default-src *.facebook.com *.fbcdn.net *.facebook.net 'self' blob:;script-src *.facebook.com *.fbcdn.net *.facebook.net blob: 'self' 'nonce-gzcsO44b';style-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob: 'unsafe-inline';connect-src *.facebook.com facebook.com *.fbcdn.net *.facebook.net wss://*.facebook.com:* wss://*.fbcdn.net attachment.fbsbx.com *.cdninstagram.com blob: 'self' data: https://edge-chat.facebook.net https://edge-chat-latest.facebook.net wss://edge-chat-latest.facebook.net wss://edge-chat.facebook.net wss://edge-chat.socialplugin.facebook.net wss://edge-chat-latest.socialplugin.facebook.net https://edge-chat.socialplugin.facebook.net https://edge-chat-latest.socialplugin.facebook.net;font-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;img-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;media-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;child-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;frame-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;manifest-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;object-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;worker-src *.facebook.com *.fbcdn.net *.facebook.net 'self' data: blob:;block-all-mixed-content;upgrade-insecure-requests;report-uri https://www.facebook.com/csp/reporting/?m=c&minimize=0;
cache-control
public, max-age=1200
timing-allow-origin
*
cross-origin-opener-policy
same-origin-allow-popups
x-fb-connection-quality
EXCELLENT; q=0.9, rtt=48, rtx=0, c=131, mss=1232, tbw=380983, tp=329, tpl=0, uplat=435, ullat=1
pragma
public
x-fb-debug
Bbb3mSshnoSHSvZAFb24osdJH5EJyXWkxfc4rnp5CEOsco/J3mp0zZS3aPaJZyyyPViTxLYe3NrFf470w3DMeA==
cross-origin-resource-policy
cross-origin
permissions-policy
accelerometer=(), attribution-reporting=(), autoplay=(), bluetooth=(), camera=(), ch-device-memory=(), ch-downlink=(), ch-dpr=(), ch-ect=(), ch-rtt=(), ch-save-data=(), ch-ua-arch=(), ch-ua-bitness=(), ch-viewport-height=(), ch-viewport-width=(), ch-width=(), clipboard-read=(), clipboard-write=(), compute-pressure=(), display-capture=(), encrypted-media=(), fullscreen=(self), gamepad=(), geolocation=(), gyroscope=(), hid=(), idle-detection=(), interest-cohort=(), keyboard-map=(), local-fonts=(), magnetometer=(), microphone=(), midi=(), otp-credentials=(), payment=(), picture-in-picture=(), private-state-token-issuance=(), publickey-credentials-get=(), screen-wake-lock=(), serial=(), shared-storage=(), shared-storage-select-url=(), private-state-token-redemption=(), usb=(), unload=(self), window-management=(), xr-spatial-tracking=();report-to="permissions_policy"
document-policy
force-load-at-top, include-js-call-stacks-in-crash-reports
x-xss-protection
0
origin-agent-cluster
?1
POST
H3
200
/ Show response
www.facebook.com/tr/ Frame 2CF3
0
20 B
128ms
50ms
Document
text/plain
57.144.244.1
Facebook
General
Full URL
https://www.facebook.com/tr/
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
57.144.244.1 Frankfurt am Main, Germany, ASN32934 (FACEBOOK - Facebook, Inc., US),
Reverse DNS
edge-star-mini-shv-01-fra5.facebook.com
Software
proxygen-bolt /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains

Request headers

Content-Type
application/x-www-form-urlencoded
Origin
https://daftarslotterpercayaidn.com
Referer
https://daftarslotterpercayaidn.com/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

access-control-allow-credentials
true
access-control-allow-origin
https://daftarslotterpercayaidn.com
alt-svc
h3=":443"; ma=86400
content-length
0
content-type
text/plain
cross-origin-resource-policy
cross-origin
date
Wed, 07 Oct 2026 05:00:09 GMT
priority
u=0,i
server
proxygen-bolt
strict-transport-security
max-age=31536000; includeSubDomains
x-fb-connection-quality
EXCELLENT; q=0.9, rtt=49, rtx=0, c=23, mss=1232, tbw=4992, tp=9, tpl=0, uplat=7, ullat=7
GET
H2
200
identify_0504602d.js Show response
analytics.tiktok.com/i18n/pixel/static/
152 KB
39 KB
64ms
63ms
Script
application/javascript
92.123.104.175
AKAMAI-ASN1 Akama...
General
Full URL
https://analytics.tiktok.com/i18n/pixel/static/identify_0504602d.js
Requested by
Host: analytics.tiktok.com
URL: https://analytics.tiktok.com/i18n/pixel/static/main.MWU2MzIzODM0MQ.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
92.123.104.175 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a92-123-104-175.deploy.static.akamaitechnologies.com
Software
nginx /
Resource Hash
417c2fa4ff8cf5e36b1797c558e99b797cf8e9a960ce8e126ccd8de6ff09efca

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

x-cache
TCP_MEM_HIT from a23-67-40-56.deploy.akamaitechnologies.com (AkamaiGHost/22.6.4-888a2d21768272d5e2d80e9762941e76) (-)
vary
Accept-Encoding
cache-control
public, max-age=31536000, immutable
content-encoding
gzip
cross-origin-resource-policy
cross-origin
x-tt-trace-tag
id=16;cdn-cache=hit;type=static
server-timing
cdn-cache; desc=HIT, edge; dur=0, origin; dur=0, inner; dur=16
x-tt-trace-id
00-2609160813255577FA96236DE53B870D-37E00633FCD35C26-00
content-length
39784
date
Wed, 07 Oct 2026 05:00:09 GMT
content-type
application/javascript; charset=UTF-8
x-tt-logid
202609160813255577FA96236DE53B870D
server
nginx
x-akamai-request-id
a805f84
x-tt-trace-host
01f8c978d2ba5e65137c427b3895e12408a4945e6a0f30cd8bbd334bf166ee0cde684fb0939498b9bc9b14e62827ed9b5fbc68c6a3839d1fb328c08e033fbb2e5a2e12d5148015bc79cf58828775611f0ef9d59558a3531a85a874767bdacf472a
POST
H2
200
enrich_ipv6
analytics-ipv6.tiktokw.us/ipv6/
0
984 B
316ms
176ms
Ping
text/plain
2.16.10.92
AKAMAI-ASN1 Akama...
General
Full URL
https://analytics-ipv6.tiktokw.us/ipv6/enrich_ipv6
Requested by
Host: analytics.tiktok.com
URL: https://analytics.tiktok.com/i18n/pixel/static/main.MWU2MzIzODM0MQ.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
2.16.10.92 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a2-16-10-92.deploy.static.akamaitechnologies.com
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Security Headers
Name Value
Strict-Transport-Security max-age=31536000 ; includeSubDomains

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

x-cache-remote
TCP_MISS from a23-213-246-176.deploy.akamaitechnologies.com (AkamaiGHost/22.6.4-f482a3e3664c9c221e0e3f27d57156e9) (-)
access-control-allow-methods
GET,POST,PUT,PATCH,DELETE,HEAD,OPTIONS,UPDATE
expires
Wed, 07 Oct 2026 05:00:09 GMT
server-timing
cdn-cache; desc=MISS, edge; dur=87, origin; dur=39, inner; dur=13
x-cache
TCP_MISS from a23-41-167-93.deploy.akamaitechnologies.com (AkamaiGHost/22.6.4-f482a3e3664c9c221e0e3f27d57156e9) (-)
date
Wed, 07 Oct 2026 05:00:09 GMT
x-akamai-request-id
64e333e6.20da73a8
access-control-allow-headers
Authorization,*
x-tt-trace-host
0165538117549bae1741fafe83dbf425744cffb3294abe9da9a65356d531fd05f17580478f0605d0d10ee36b81e847e68b27b67870de4815cd339b20aaf238b163fba089dd6ca44a8166fbc6dfe750cf49c58b3c16cd243fdd3a2c1731bbb140fd69399d440272e2ba516145b9f1f9cd5c0f2d849896e20f937bb962e244d45be793fefd601fdd31b11797ab10e877fb77
strict-transport-security
max-age=31536000 ; includeSubDomains
x-origin-response-time
39,23.213.246.176
cache-control
max-age=0, no-cache, no-store
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-tt-trace-tag
id=16;cdn-cache=miss;type=dyn
access-control-allow-origin
*
x-tt-trace-id
00-261007050009792919A1D4FC3813BE32-2B4176DB1AD26128-00
content-length
0
x-parent-response-time
126,23.41.167.93
x-tt-logid
20261007050009792919A1D4FC3813BE32
server
nginx
POST
H2
200
pixel
analytics.tiktok.com/api/v2/
0
951 B
190ms
187ms
Ping
text/plain
92.123.104.175
AKAMAI-ASN1 Akama...
General
Full URL
https://analytics.tiktok.com/api/v2/pixel
Requested by
Host: analytics.tiktok.com
URL: https://analytics.tiktok.com/i18n/pixel/static/main.MWU2MzIzODM0MQ.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
92.123.104.175 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a92-123-104-175.deploy.static.akamaitechnologies.com
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

x-cache-remote
TCP_MISS from a23-218-223-82.deploy.akamaitechnologies.com (AkamaiGHost/22.6.4-888a2d21768272d5e2d80e9762941e76) (-)
access-control-allow-methods
GET,POST,PUT,PATCH,DELETE,HEAD,OPTIONS,UPDATE
expires
Wed, 07 Oct 2026 05:00:09 GMT
server-timing
cdn-cache; desc=MISS, edge; dur=97, origin; dur=22, inner; dur=14
x-cache
TCP_MISS from a23-67-40-56.deploy.akamaitechnologies.com (AkamaiGHost/22.6.4-888a2d21768272d5e2d80e9762941e76) (-)
date
Wed, 07 Oct 2026 05:00:09 GMT
x-akamai-request-id
794ec555.a805f95
access-control-allow-headers
Authorization,*
x-tt-trace-host
0165538117549bae1741fafe83dbf425740d63b9229b953d9623bc9c46304778dd589a0ad72d72c026ae261012fe33575bbfe0c78f6960cb445d8683ce1d0661c2db690ca67b5dc44ad4c0534498d0c2c5127dc36d1902406f90bd68c811a6933160a22877b661efdefdd3d683ce714037581a328025652c4ed9f95dabf3959714b3a12c4b06e963599641867afe3c509c
x-origin-response-time
22,23.218.223.82
cache-control
max-age=0, no-cache, no-store
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-tt-trace-tag
id=16;cdn-cache=miss;type=dyn
access-control-allow-origin
*
x-tt-trace-id
00-261007050009AEAFF3CA4A046B810FBC-43B840651FE55BBE-00
content-length
0
x-parent-response-time
112,23.67.40.56
x-tt-logid
20261007050009AEAFF3CA4A046B810FBC
server
nginx
POST
H2
200
pixel
analytics.tiktok.com/api/v2/
0
924 B
217ms
214ms
Ping
text/plain
92.123.104.175
AKAMAI-ASN1 Akama...
General
Full URL
https://analytics.tiktok.com/api/v2/pixel
Requested by
Host: analytics.tiktok.com
URL: https://analytics.tiktok.com/i18n/pixel/static/main.MWU2MzIzODM0MQ.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
92.123.104.175 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a92-123-104-175.deploy.static.akamaitechnologies.com
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

x-cache-remote
TCP_MISS from a23-3-12-94.deploy.akamaitechnologies.com (AkamaiGHost/22.6.4-888a2d21768272d5e2d80e9762941e76) (-)
access-control-allow-methods
GET,POST,PUT,PATCH,DELETE,HEAD,OPTIONS,UPDATE
expires
Wed, 07 Oct 2026 05:00:09 GMT
server-timing
cdn-cache; desc=MISS, edge; dur=100, origin; dur=23, inner; dur=18
x-cache
TCP_MISS from a23-67-40-56.deploy.akamaitechnologies.com (AkamaiGHost/22.6.4-888a2d21768272d5e2d80e9762941e76) (-)
date
Wed, 07 Oct 2026 05:00:09 GMT
x-akamai-request-id
fdd143e5.a805f96
access-control-allow-headers
Authorization,*
x-tt-trace-host
0165538117549bae1741fafe83dbf425740d63b9229b953d9623bc9c46304778ddf87fc49b5f6a084d69da687f95c5bf92dad3ce52a3348efc0d90c9fe98212cfe0e0adcf4acd448f51e66c6d671aaf2a2e740ccabded0be043e8b7d471477e60a503667385515d2f07b325bde502d5f6221962cfa732c154ca7992aae8c98f5b6
x-origin-response-time
23,23.3.12.94
cache-control
max-age=0, no-cache, no-store
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-tt-trace-tag
id=16;cdn-cache=miss;type=dyn
access-control-allow-origin
*
x-tt-trace-id
00-261007050009FB12B429DE9C09BE7A58-7AFB152627A76ADB-00
content-length
0
x-parent-response-time
116,23.67.40.56
x-tt-logid
20261007050009FB12B429DE9C09BE7A58
server
nginx
GET
H2
200
/
rt.flix360.com/beat/
43 B
162 B
345ms
158ms
Image
image/gif
63.34.183.36
Amazon.com
General
Full URL
https://rt.flix360.com/beat/?newtrackv2&ver=v2&ts=wildcard&d=12612&l=id&et=wildcard_failure&vtime=0&gvid=flix8d80a3a09720d526f8ca0b32.bd6fd332&cs=true&cp=&cd=&sid=21887416-9961-67E2-7319-46A1639921A1&device=desktop&ed=&ism=false&l1=id&l2=e2&p=0&br=Tropicana%20Slim&price=20.00&ref=&currency=&pn=https%3A%2F%2Fdaftarslotterpercayaidn.com%2F&h1=&ti=RAKYATJP%3A%20Rahasia%20Jam%20Gacor%20Slot%20Biar%20Cepat%20Maxwin&img=https%3A%2F%2Fgen.blackmolesamp.com%2Fuploads%2Frakyatjp-rahasia-jam-gacor-slot-biar-cep-1791348974924-40e3c76a1a82.png&r1.cat=&om=&mpn=749921021090&ean=NUT-60023-01292&ut=1791342009238&cb=1791342009238&ref=
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
63.34.183.36 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-63-34-183-36.eu-west-1.compute.amazonaws.com
Software
/
Resource Hash
aa03dc59bdca72631d2301e4297cfa030bd31b907dc138e7b973d12311c90a22

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

apigw-requestid
E226DitQjoEEJQQ=
cache-control
max-age=157680000000
content-length
43
date
Wed, 07 Oct 2026 05:00:09 GMT
content-type
image/gif
POST
H2
200
act
analytics.tiktok.com/api/v2/pixel/
0
949 B
444ms
439ms
Ping
text/plain
92.123.104.175
AKAMAI-ASN1 Akama...
General
Full URL
https://analytics.tiktok.com/api/v2/pixel/act
Requested by
Host: analytics.tiktok.com
URL: https://analytics.tiktok.com/i18n/pixel/static/main.MWU2MzIzODM0MQ.js
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
92.123.104.175 Frankfurt am Main, Germany, ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL),
Reverse DNS
a92-123-104-175.deploy.static.akamaitechnologies.com
Software
nginx /
Resource Hash
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

x-cache-remote
TCP_MISS from a23-3-12-78.deploy.akamaitechnologies.com (AkamaiGHost/22.6.4-888a2d21768272d5e2d80e9762941e76) (-)
access-control-allow-methods
GET,POST,PUT,PATCH,DELETE,HEAD,OPTIONS,UPDATE
expires
Wed, 07 Oct 2026 05:00:09 GMT
server-timing
cdn-cache; desc=MISS, edge; dur=99, origin; dur=242, inner; dur=29
x-cache
TCP_MISS from a23-67-40-56.deploy.akamaitechnologies.com (AkamaiGHost/22.6.4-888a2d21768272d5e2d80e9762941e76) (-)
date
Wed, 07 Oct 2026 05:00:09 GMT
x-akamai-request-id
6dfecdb1.a80601a
access-control-allow-headers
Authorization,*
x-tt-trace-host
0165538117549bae1741fafe83dbf425740d63b9229b953d9623bc9c46304778dd3bd514de5e4306af8ba25a63bcc08510544e95110e88c90bf714e8666b424cc39525395422b46d12338a5cdb75754e5449d461198c71c701aabf97e99c7bf0a3af413a22e837ad31f52e5820af6832df35dca78dbfbe3bd85bfff765320400fcc2d57cac6c0af0eb39089eaf6c1c5406
x-origin-response-time
242,23.3.12.78
cache-control
max-age=0, no-cache, no-store
pragma
no-cache
cross-origin-resource-policy
cross-origin
x-tt-trace-tag
id=16;cdn-cache=miss;type=dyn
access-control-allow-origin
*
x-tt-trace-id
00-261007050009B9A4B863776353D439B7-108E1D7D1EF16C26-00
content-length
0
x-parent-response-time
331,23.67.40.56
x-tt-logid
20261007050009B9A4B863776353D439B7
server
nginx
GET
H2
200
websdksettings Show response
sdk-01.moengage.com/v2/
3 KB
1 KB
152ms
152ms
XHR
application/json
3.161.82.25
Amazon.com
General
Full URL
https://sdk-01.moengage.com/v2/websdksettings?app_id=QTD7QXC51X5DZR3CTIHK33PQ
Requested by
Host: cdn.moengage.com
URL: https://cdn.moengage.com/webpush/moe_webSdk.min.latest.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.25 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-25.fra56.r.cloudfront.net
Software
nginx /
Resource Hash
adaddbdb405b4cb59988b54dd6e446f5b0c3359f87d4536f567b2d36dd60aefc

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache
content-encoding
gzip
access-control-allow-credentials
true
access-control-allow-methods
GET, POST, OPTIONS
via
1.1 3c13cc51908e4d37d2a5046d7703e256.cloudfront.net (CloudFront)
expires
Wed, 07 Oct 2026 05:00:09 GMT
access-control-allow-origin
*
x-cache
Miss from cloudfront
x-amz-cf-id
3FT4mIX0vRkRpjXfA9bWvMAuavB7pFprSCVWLkVctyn2XD7UmqKJ_g==
date
Wed, 07 Oct 2026 05:00:10 GMT
content-type
application/json
vary
Accept-Encoding
server
nginx
x-amz-cf-pop
FRA56-P10
access-control-allow-headers
DNT,X-CustomHeader,Keep-Alive,User-Agent,X-Requested-With,If-Modified-Since,Cache-Control,Content-Type
POST
H2
200
QTD7QXC51X5DZR3CTIHK33PQ Show response
sdk-01.moengage.com/v3/sdkconfig/web/
694 B
871 B
180ms
179ms
XHR
application/json
3.161.82.25
Amazon.com
General
Full URL
https://sdk-01.moengage.com/v3/sdkconfig/web/QTD7QXC51X5DZR3CTIHK33PQ
Requested by
Host: cdn.moengage.com
URL: https://cdn.moengage.com/webpush/moe_webSdk.min.latest.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.25 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-25.fra56.r.cloudfront.net
Software
nginx /
Resource Hash
2fa614ac18e2af5676a7bc9cebb918990484ebf124765a96c5fdfb9de8ff5a24

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

cache-control
no-cache
content-encoding
gzip
access-control-allow-credentials
true
access-control-allow-methods
GET, POST, OPTIONS
via
1.1 3c13cc51908e4d37d2a5046d7703e256.cloudfront.net (CloudFront)
expires
Wed, 07 Oct 2026 05:00:09 GMT
access-control-allow-origin
*
x-cache
Miss from cloudfront
x-amz-cf-id
i_i-1zKuMio2soZfBueu9PpYn4vCsDibXdFVeB7byHCGZmJBZz8zMw==
date
Wed, 07 Oct 2026 05:00:10 GMT
content-type
application/json
vary
Accept-Encoding
server
nginx
x-amz-cf-pop
FRA56-P10
access-control-allow-headers
DNT,X-CustomHeader,Keep-Alive,User-Agent,X-Requested-With,If-Modified-Since,Cache-Control,Content-Type
GET
H2
200
destination Show response
www.googletagmanager.com/gtag/
431 KB
150 KB
69ms
69ms
Script
application/javascript
192.178.183.97
Google LLC
General
Full URL
https://www.googletagmanager.com/gtag/destination?id=AW-925089264&cx=c&gtm=4e6a51
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtm.js?id=GTM-TKQZL95
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
192.178.183.97 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfraw-in-f97.1e100.net
Software
Google Tag Manager /
Resource Hash
855fd1491666c31b8b181330a959ce2fed48235696368901f7d8488bd53eb5bf
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
zstd
report-to
{"group":"ascgsrsghrgc:71:0","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/scaffolding/ascgsrsghrgc:71:0"}],}
expires
Wed, 07 Oct 2026 05:00:10 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 07 Oct 2026 05:00:10 GMT
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
access-control-allow-headers
Cache-Control
strict-transport-security
max-age=31536000; includeSubDomains
cache-control
private, max-age=900
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
content-security-policy-report-only
script-src 'none'; form-action 'none'; frame-src 'none'; report-uri https://csp.withgoogle.com/csp/scaffolding/ascgsrsghrgc:71:0
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to=ascgsrsghrgc:71:0
content-length
153100
x-xss-protection
0
server
Google Tag Manager
GET
H2
200
destination Show response
www.googletagmanager.com/gtag/
431 KB
150 KB
84ms
83ms
Script
application/javascript
192.178.183.97
Google LLC
General
Full URL
https://www.googletagmanager.com/gtag/destination?id=AW-920334631&cx=c&gtm=4e6a51
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtm.js?id=GTM-TKQZL95
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
192.178.183.97 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
lcfraw-in-f97.1e100.net
Software
Google Tag Manager /
Resource Hash
6b9039b8c10a3fcac130a6e154fa127cd40f039e7b58abe6200f1925e4bc625b
Security Headers
Name Value
Strict-Transport-Security max-age=31536000; includeSubDomains
X-Xss-Protection 0

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

content-encoding
zstd
report-to
{"group":"ascgsrsghrgc:71:0","max_age":2592000,"endpoints":[{"url":"https://csp.withgoogle.com/csp/report-to/scaffolding/ascgsrsghrgc:71:0"}],}
expires
Wed, 07 Oct 2026 05:00:10 GMT
alt-svc
h3=":443"; ma=2592000,h3-29=":443"; ma=2592000
date
Wed, 07 Oct 2026 05:00:10 GMT
content-type
application/javascript; charset=UTF-8
vary
Accept-Encoding
access-control-allow-headers
Cache-Control
strict-transport-security
max-age=31536000; includeSubDomains
cache-control
private, max-age=900
cross-origin-resource-policy
cross-origin
access-control-allow-credentials
true
content-security-policy-report-only
script-src 'none'; form-action 'none'; frame-src 'none'; report-uri https://csp.withgoogle.com/csp/scaffolding/ascgsrsghrgc:71:0
access-control-allow-origin
*
cross-origin-opener-policy-report-only
same-origin; report-to=ascgsrsghrgc:71:0
content-length
153101
x-xss-protection
0
server
Google Tag Manager
GET
H2
204
tags
asia.creativecdn.com/ Frame CE51
0
0
207ms
206ms
Document
text/plain
103.132.192.30
RTB HOUSE PTE. LTD.
General
Full URL
https://asia.creativecdn.com/tags?id=pr_FAOiA95ZI30AXifJGDUt_home&id=pr_FAOiA95ZI30AXifJGDUt_uid_unknown
Requested by
Host: daftarslotterpercayaidn.com
URL: https://daftarslotterpercayaidn.com/
Protocol
H2
Security
TLS 1.3, , AES_256_GCM
Server
103.132.192.30 , Singapore, ASN138552 (RTBHOUSE-AS-AP - RTB HOUSE PTE. LTD., SG),
Reverse DNS
ip-103-132-192-30.rtbhouse.net
Software
/
Resource Hash

Request headers

Referer
https://daftarslotterpercayaidn.com/
Upgrade-Insecure-Requests
1
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0
sec-ch-ua-platform
"Linux"

Response headers

GET
H3
200
7082.js Show response
script.crazyegg.com/pages/scripts/0075/
9 KB
223 B
36ms
36ms
Script
text/javascript
104.19.147.8
Cloudflare
General
Full URL
https://script.crazyegg.com/pages/scripts/0075/7082.js
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtm.js?id=GTM-TKQZL95
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
104.19.147.8 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
e2f36a32e1ba4787a3391b7a670fa43a9bec7431f4823774344b68c398eed905

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

access-control-expose-headers
CE-Version
content-encoding
gzip
cf-cache-status
HIT
age
3441
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Wed, 07 Oct 2026 05:00:10 GMT
content-type
text/javascript
last-modified
Wed, 07 Oct 2026 04:02:48 GMT
vary
accept-encoding
priority
u=3,i=?0
cache-control
public, max-age=300, s-maxage=1209600
timing-allow-origin
*
cf-ray
a46a5732890fbf47-WAW
accept-ranges
bytes
access-control-allow-origin
*
content-length
3105
ce-version
11.5.557
server
cloudflare
GET
H3
200
customer-care-button-blibli.png
www.static-src.com/siva/asset/09_2024/
9 KB
9 KB
368ms
368ms
Image
image/png
34.117.1.79
Google LLC
General
Full URL
https://www.static-src.com/siva/asset/09_2024/customer-care-button-blibli.png
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
34.117.1.79 Kansas City, United States, ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US),
Reverse DNS
79.1.117.34.bc.googleusercontent.com
Software
openresty /
Resource Hash
0acbc669c7d0ad6ebea3858b6c1c6ee2fd335ec89dedb84d14190d0c12c85be2

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

x-goog-metageneration
1
x-robots-tag
index
x-goog-hash
crc32c=Wocmag==, md5=jpu9Mt1MtXvbkXR353zQag==
etag
"8e9bbd32dd4cb57bdb917477e77cd06a"
x-goog-stored-content-encoding
identity
x-width-folder
original
expires
Thu, 07 Oct 2027 05:00:10 GMT
alt-svc
h3=":443"; ma=2592000
x-goog-stored-content-length
9458
date
Wed, 07 Oct 2026 05:00:10 GMT
content-type
png
last-modified
Wed, 18 Sep 2024 06:13:30 GMT
vary
Accept
x-guploader-uploadid
AP6rU80rp7vxTkOxAL8r-bOx5pnPmJW8x_pNjUMlHNa0HmKAzENW31xompVgVExUFYY1My-d
x-cache-status
HIT
cache-control
max-age=31536000, public, max-age=31536000
x-goog-storage-class
STANDARD
via
1.1 google
x-cache-key
/siva/asset/09_2024/customer-care-button-blibli.png?w=original:resized:png
x-upstream-url
storage.googleapis.com/engagement-services-prod/siva/asset/09_2024/customer-care-button-blibli.png
accept-ranges
bytes
access-control-allow-origin
https://www.blibli.com
x-goog-generation
1726640010941519
content-length
9458
x-delivery-format
png
server
openresty
POST
H3
404
rum Show response
daftarslotterpercayaidn.com/cdn-cgi/
151 B
651 B
36ms
35ms
XHR
text/html
172.67.155.237
Cloudflare
General
Full URL
https://daftarslotterpercayaidn.com/cdn-cgi/rum?
Requested by
Host: static.cloudflareinsights.com
URL: https://static.cloudflareinsights.com/beacon.min.js/v8c78df7c7c0f484497ecbca7046644da1771523124516
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
172.67.155.237 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
d66dd0f2f24c4343661a5396e1ba76782fe651f7d422209eded956ebf90900fc
Security Headers
Name Value
X-Frame-Options SAMEORIGIN

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
content-type
application/json
sec-ch-ua-mobile
?0

Response headers

cache-control
private, max-age=0, no-store, no-cache, must-revalidate, post-check=0, pre-check=0
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
content-encoding
zstd
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=SSSdpmawnqgYXuptkEDKFjvitPG896s65%2BejSknHineiAzWxPDm5Y0RW8Qaa7FPeKe0Sj3GTCAZdO9i4e0ig1elhcEwOdjKQ3tofseqcEr3x1h9MOWptViP%2BLar2JWIw%2BkWXDjRgf0NKnx9mzg0%3D"}]}
referrer-policy
same-origin
cf-ray
a46a573299229d75-WAW
expires
Thu, 01 Jan 1970 00:00:01 GMT
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
date
Wed, 07 Oct 2026 05:00:10 GMT
content-type
text/html; charset=UTF-8
server
cloudflare
priority
u=1,i
x-frame-options
SAMEORIGIN
GET
H3
200
iconrakyatjp.webp
meubelkayumurah.pics/wp-content/uploads/2026/05/
2 KB
0
2ms
2ms
Other
image/webp
188.114.97.3
Cloudflare
General
Full URL
https://meubelkayumurah.pics/wp-content/uploads/2026/05/iconrakyatjp.webp
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
188.114.97.3 , Ascension Island, ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US),
Reverse DNS
Software
cloudflare /
Resource Hash
3064c443efe71ba06a3aa0a60a29fb67ed9b49a55597a61b2f23eb345567ffb3

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

cache-control
max-age=14400
nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
cf-cache-status
HIT
age
1816
report-to
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=DV1urVIWRADSsRlmxZsbcxVvq4Eypshq6oeuPtYAcwiKBtgqdzvhF9lEeVf%2FNfidEm9LNFi8CcrbdbM6Kysk6WaHd5Ni6qsGZIddWJGD5SUh42iaVSlCi2Xjmk%2FIi9AkDGu5RVJF7g%3D%3D"}]}
cf-ray
a46a57249991cf5c-WAW
accept-ranges
bytes
alt-svc
h3=":443"; ma=86400
server-timing
cfExtPri
content-length
2334
date
Wed, 07 Oct 2026 05:00:07 GMT
content-type
image/webp
last-modified
Mon, 18 May 2026 11:14:58 GMT
server
cloudflare
priority
u=3,i
POST
H3
200
collect
www.google.com/ccm/
0
0
49ms
49ms
Fetch
text/plain
142.251.156.119
Google LLC
General
Full URL
https://www.google.com/ccm/collect?rcb=7&frm=0&apvc=0&ae=g&auid=677347693.1791349208&dt=RAKYATJP%3A%20Rahasia%20Jam%20Gacor%20Slot%20Biar%20Cepat%20Maxwin&tid=AW-925089264&dl=https%3A%2F%2Fdaftarslotterpercayaidn.com%2F&scrsrc=www.googletagmanager.com&rnd=1416088682.1791349208&navt=n&npa=1&ep.ecomm_pagetype=home&_tu=CA&gtm=45be6a51z8810058345za20gzb810058345zd810058345xeaxf1&gcd=13l3l3l2l1l1&dma_cps=a&dma=1&tag_exp=115616985~115938466~115938469~118897920~118897930~120213116~120385423~120469145~120469153~121046263~121046271~121280969&tft=1791349210145&tfd=3802&tids=AW-925089264&fmt=8
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtag/destination?id=AW-925089264&cx=c&gtm=4e6a51
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.156.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
/
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

POST
H3
200
collect
www.google.com/ccm/
0
0
49ms
49ms
Fetch
text/plain
142.251.156.119
Google LLC
General
Full URL
https://www.google.com/ccm/collect?rcb=11&frm=0&apvc=0&ae=g&auid=677347693.1791349208&dt=RAKYATJP%3A%20Rahasia%20Jam%20Gacor%20Slot%20Biar%20Cepat%20Maxwin&tid=AW-920334631&dl=https%3A%2F%2Fdaftarslotterpercayaidn.com%2F&scrsrc=www.googletagmanager.com&rnd=1416088682.1791349208&navt=n&npa=1&ep.ecomm_pagetype=retail-home&_tu=CA&gtm=45be6a51z8810058345za20gzb810058345zd810058345xeaxf1&gcd=13l3l3l2l1l1&dma_cps=a&dma=1&tag_exp=115938466~115938468~118897920~118897930~120032690~120213116~120385422~120420415~120469145~120469153~121046263~121046271~121280969~121427142&tft=1791349210187&tfd=3843&tids=AW-920334631&fmt=8
Requested by
Host: www.googletagmanager.com
URL: https://www.googletagmanager.com/gtag/destination?id=AW-920334631&cx=c&gtm=4e6a51
Protocol
H3
Security
QUIC, , AES_128_GCM
Server
142.251.156.119 , United States, ASN15169 (GOOGLE - Google LLC, US),
Reverse DNS
Software
/
Resource Hash

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

POST
H2
200
add Show response
sdk-01.moengage.com/v2/device/
91 B
486 B
200ms
198ms
XHR
application/json
3.161.82.25
Amazon.com
General
Full URL
https://sdk-01.moengage.com/v2/device/add?os=web&os_platform=Mozilla%2F5.0%20(X11%3B%20Linux%20x86_64)%20AppleWebKit%2F537.36%20(KHTML%2C%20like%20Gecko)%20Chrome%2F154.0.0.0%20Safari%2F537.36&is_incognito=false&app_id=QTD7QXC51X5DZR3CTIHK33PQ&os_ver=Linux&sdk_ver=2.81.00&model=Google%20Chrome&app_ver=1.0&device_ts=1791349210196&device_tz_offset=7200000&unique_id=55c947f7-9133-43f8-88b6-0e142b0c732e&device_tz=-120&device_unique_id=200e9e96-a815-4f5f-b665-b6fc81f2ce12&subscription_type=vapid&vapid_public=BFrANqB3uqa5scQrpht4tHIxVAbHrY8MiHXu9MXb8UoaKwECZDNVvZfMFEoCbrlynMMxNV2FzCpp1uT1A-It16w&url=https%3A%2F%2Fdaftarslotterpercayaidn.com%2F
Requested by
Host: cdn.moengage.com
URL: https://cdn.moengage.com/webpush/moe_webSdk.min.latest.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.25 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-25.fra56.r.cloudfront.net
Software
envoy /
Resource Hash
8d6b712cd54b8b0c809ed2daa5b35913f5fb92fdb2e643b0e754227068d0f088

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
Content-Type
text/plain;charset=UTF-8
sec-ch-ua-mobile
?0

Response headers

content-encoding
gzip
x-envoy-upstream-service-time
36
x-ratelimit-reset
1
via
1.1 3c13cc51908e4d37d2a5046d7703e256.cloudfront.net (CloudFront)
x-ratelimit-remaining
9995
access-control-allow-origin
*
x-cache
Miss from cloudfront
x-amz-cf-id
aVGsULDlDqe3HSCt4jPjOPZJWl2pDTQYttaWhP-rTzbo2zEhCV92jQ==
date
Wed, 07 Oct 2026 05:00:10 GMT
x-ratelimit-limit
10000, 10000;w=1
content-type
application/json
vary
accept-encoding
server
envoy
x-amz-cf-pop
FRA56-P10
GET
H2
200
/
rt.flix360.com/beat/
43 B
161 B
101ms
100ms
Image
image/gif
63.34.183.36
Amazon.com
General
Full URL
https://rt.flix360.com/beat/?newtrackv2&ver=v2&ts=traffic&d=12612&l=id&et=traffic&vtime=0&gvid=flix8d80a3a09720d526f8ca0b32.bd6fd332&cs=true&cp=&cd=&sid=21887416-9961-67E2-7319-46A1639921A1&device=desktop&ed=&ism=false&l1=id&l2=e2&p=0&br=Tropicana%20Slim&price=20.00&ref=&currency=&pn=https%3A%2F%2Fdaftarslotterpercayaidn.com%2F&h1=&ti=RAKYATJP%3A%20Rahasia%20Jam%20Gacor%20Slot%20Biar%20Cepat%20Maxwin&img=https%3A%2F%2Fgen.blackmolesamp.com%2Fuploads%2Frakyatjp-rahasia-jam-gacor-slot-biar-cep-1791348974924-40e3c76a1a82.png&r1.cat=&om=&mpn=749921021090&ean=NUT-60023-01292&ut=1791342010239&cb=1791342010239&ref=
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
63.34.183.36 Dublin, Ireland, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
ec2-63-34-183-36.eu-west-1.compute.amazonaws.com
Software
/
Resource Hash
aa03dc59bdca72631d2301e4297cfa030bd31b907dc138e7b973d12311c90a22

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
sec-ch-ua-mobile
?0

Response headers

apigw-requestid
E226LhzAjoEEJTQ=
cache-control
max-age=157680000000
content-length
43
date
Wed, 07 Oct 2026 05:00:10 GMT
content-type
image/gif
POST
H2
200
live Show response
sdk-01.moengage.com/v3/campaigns/inapp/
2 KB
1 KB
169ms
168ms
XHR
application/json
3.161.82.25
Amazon.com
General
Full URL
https://sdk-01.moengage.com/v3/campaigns/inapp/live?sdk_ver=2.81.00&unique_id=55c947f7-9133-43f8-88b6-0e142b0c732e&os=web
Requested by
Host: cdn.moengage.com
URL: https://cdn.moengage.com/webpush/moe_webSdk.min.latest.js
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.25 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-25.fra56.r.cloudfront.net
Software
/
Resource Hash
66ab1cdce2c0f27f6127b7da1d318aeb7994d650f78080aff1f969ec515aa3d1

Request headers

sec-ch-ua-platform
"Linux"
Referer
https://daftarslotterpercayaidn.com/
MOE-APPKEY
QTD7QXC51X5DZR3CTIHK33PQ
sec-ch-ua
"Chromium";v="154", "Google Chrome";v="154", "Not A(Brand";v="99"
Content-Type
application/json
sec-ch-ua-mobile
?0
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36

Response headers

content-encoding
gzip
via
1.1 3c13cc51908e4d37d2a5046d7703e256.cloudfront.net (CloudFront)
access-control-allow-origin
*
x-cache
Miss from cloudfront
moe-request-id
fb104e53-1d4c-46ef-b9e9-ccd5f8453e7d
x-amz-cf-id
OWfHFDeY1gxLxVdNb9sgh2rkReexeCJLPpQJvCaiov3HEPAEmjhe5w==
date
Wed, 07 Oct 2026 05:00:10 GMT
content-type
application/json
vary
origin,access-control-request-method,access-control-request-headers,accept-encoding
x-amz-cf-pop
FRA56-P10
OPTIONS
H2
200
live
sdk-01.moengage.com/v3/campaigns/inapp/ Frame
0
0
143ms
143ms
Preflight
3.161.82.25
Amazon.com
General
Full URL
https://sdk-01.moengage.com/v3/campaigns/inapp/live?sdk_ver=2.81.00&unique_id=55c947f7-9133-43f8-88b6-0e142b0c732e&os=web
Protocol
H2
Security
TLS 1.3, , AES_128_GCM
Server
3.161.82.25 , United States, ASN16509 (AMAZON-02 - Amazon.com, Inc., US),
Reverse DNS
server-3-161-82-25.fra56.r.cloudfront.net
Software
/
Resource Hash

Request headers

Accept
*/*
Access-Control-Request-Headers
content-type,moe-appkey
Access-Control-Request-Method
POST
Origin
https://daftarslotterpercayaidn.com
Sec-Fetch-Mode
cors
User-Agent
Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/154.0.0.0 Safari/537.36

Response headers

access-control-allow-headers
content-type, moe-appkey
access-control-allow-methods
POST,OPTIONS
access-control-allow-origin
*
access-control-max-age
3600
content-length
0
date
Wed, 07 Oct 2026 05:00:10 GMT
moe-request-id
9c138d79-c341-4f86-9d44-62d32e669c99
vary
Origin Access-Control-Request-Method Access-Control-Request-Headers
via
1.1 3c13cc51908e4d37d2a5046d7703e256.cloudfront.net (CloudFront)
x-amz-cf-id
qYrl0EzA3ojVIR3RG9a-_APmRIp2g200qXuUwQFDtncBZvWKWc5LIg==
x-amz-cf-pop
FRA56-P10
x-cache
Miss from cloudfront

Failed requests

These URLs were requested, but there was no response received. You will also see them in the list above.

Domain
www.blibli.com
URL
https://www.blibli.com/backend/content/thematic/thematic_configuration_non_canary.js
Domain
www.static-src.com
URL
https://www.static-src.com/frontend/static/js/CustomerLocation.49933ea8.js
Domain
www.static-src.com
URL
https://www.static-src.com/frontend/static/js/address-event.0a54fb2b.js
Domain
www.static-src.com
URL
https://www.static-src.com/frontend/static/js/Location.c79a4a93.js
Domain
www.static-src.com
URL
https://www.static-src.com/frontend/static/js/customer-location-mixin.dd72e66a.js
Domain
www.blibli.com
URL
https://www.blibli.com/bwa/2.4.5-0/index.js
Domain
www.static-src.com
URL
https://www.static-src.com/frontend/static/js/FootSection.709acb56.js
Domain
www.static-src.com
URL
https://www.static-src.com/frontend/static/js/AccordionContent.6cf8e4dd.js
Domain
www.static-src.com
URL
https://www.static-src.com/frontend/static/js/FooterDetail.22d2666a.js
Domain
www.static-src.com
URL
https://www.static-src.com/frontend/static/js/index.5457813a.js
Domain
www.static-src.com
URL
https://www.static-src.com/frontend/static/js/LazyImage.92de27af.js
Domain
www.static-src.com
URL
https://www.static-src.com/frontend/static/js/BlibliRouter.a4a077a8.js
Domain
www.static-src.com
URL
https://www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/js/summary-mixin.js
Domain
www.static-src.com
URL
https://www.static-src.com/frontend/static/fonts/blibli-medium-eee84661.woff2
Domain
www.static-src.com
URL
https://www.static-src.com/frontend/static/fonts/blibli-demi-bold-6dd433a2.woff2

Verdicts & Comments Add Verdict or Comment

427 JavaScript Window variables Go Pro

Only in urlscan Pro

Inspect and pivot on JavaScript variables, identifiers, and other key site metadata data with urlscan Pro. Reveal and search on client-side frameworks, runtime variables, and custom values.
Click for more information
Free trials of urlscan Pro are available.

These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.

object| 0 object| 1 object| 2 object| 3 object| 4 object| 5 object| 6 object| 7 object| 8 object| 9 object| 10 object| 11 object| 12 object| 13 object| 14 object| 15 object| _bwaq object| akcr object| dataLayer object| _spapi string| _HIDDEN_HOME_MOBILE_SECTIONS string| _HIDDEN_HOME_DESKTOP_SECTIONS string| _MCDOMO_PUBLIC_PATH string| _FLASHSALE_NEW_API string| _GROCERY_AVAILABLE string| _GROCERY_ONBOARDING string| _SCANNER_AVAILABLE string| _FB_OG_IMAGE_URL_META string| _WA_OG_IMAGE_URL_META string| _TWITTER_CARD_IMAGE_URL_META string| _MEMBER_UNM_ACTIVE_FLAG string| _MEMBER_UNM_BASE_URL string| _MEMBER_UNM_LOGIN_URL string| _MEMBER_UNM_REGISTER_URL string| _MEMBER_UNM_ACCOUNT_URL string| _MEMBER_UNM_VERIFY_URL string| _MEMBER_UNM_BLIBLI_CLIENT_ID string| _MEMBER_UNM_INFO_URL string| _MEMBER_UNM_SSO_REDIRECTION_FLAG string| _MEMBER_USE_VUE3 string| _MEMBER_GA_STREAM_ID string| _MEMBER_USE_IAM_API string| _MEMBER_AFFILIATE_PNV_URL string| _MEMBER_AFFILIATE_PNV_APPS_WEB_VIEW object| webpackChunkCE2 object| __moe object| MoeWebP object| VWO function| vwo_$ object| Wingify object| _vwo_exp_ids object| _vwo_exp string| _vwo_server_url object| _vis_opt_queue object| _vis_opt_check_segment function| getVwoCode object| _vwo_evq function| _vwo_ev boolean| DISABLE_NATIVE_CONSTANTS object| _vwo_t object| _vwo_editorOperationTracker function| _vwo_handleMutations object| _vwo_api_section_callback object| _vis_opt_comb_name object| vwo_iehack_queue boolean| hotspotwebarstatic object| product_json object| flixtracking function| logqa number| flixtrackloading object| flixJsCallbacks string| flixconsent object| FlixBrandZone function| gtag object| moeInternals object| CE2 object| CE2BH function| CE_URL_FINGERPRINT object| CE_API function| moe string| moeBannerText function| MoengagePageEventHistoryManager object| google_tag_data function| ga object| gaplugins object| impactDataLayer function| ire object| irEvent string| ENV string| flixmain_base_url string| flixmain_api_base_url string| flixmain_base_modular_url string| flixmain_api_call_url boolean| flixmain_api_call_url_dummy string| flixmain_product_id string| flixmain_distributor boolean| flixmain_abtesting boolean| flixmain_stop_tracking string| flixmain_language string| flixmain_language_fliso string| flixmain_dmn string| flixmain_button_img string| flixmain_mpn string| flixmain_ean string| flixmain_adjacent_codes string| flixmain_smart_config_id string| flixmain_HS_pos string| flixmain_HS_container string| flixRetailerUrlStore string| initialUrl object| flixurlParams object| myScript string| myScriptSrc object| serviceurl object| flixloaderjs string| flixmain_mpn_ean object| distributorIdsDE string| flixtopurl number| flixs object| flixarparser object| flixAllowedModel function| FlixjQ function| log5 function| log4 function| log3 function| log2 function| logflix object| FlixServices function| flixUAParser string| value_m string| value_n string| modurl object| google_tag_manager function| onYouTubeIframeAPIReady object| gaGlobal function| twq function| fbq function| _fbq string| campaign string| medium string| source object| _bwa object| lotame_10867 function| lotameIsCompatible function| lt10867_ba function| lt10867_b function| lt10867_ea object| lt10867_e function| lt10867_f function| lt10867_ga function| lt10867_ja object| lt10867_ object| lt10867_na object| lt10867_oa object| lt10867_q object| lt10867_Qa object| lt10867_6 function| lt10867_aa function| lt10867_a function| lt10867_d function| lt10867_fa function| lt10867_ha function| lt10867_g function| lt10867_ia function| lt10867_h function| lt10867_i function| lt10867_j function| lt10867_k function| lt10867_ka function| lt10867_l function| lt10867_m function| lt10867_n function| lt10867_o function| lt10867_la function| lt10867_ma function| lt10867_p function| lt10867_r function| lt10867_t function| lt10867_u function| lt10867_v function| lt10867_pa function| lt10867_w function| lt10867_ta function| lt10867_qa function| lt10867_ra function| lt10867_ua function| lt10867_sa function| lt10867_va function| lt10867_x function| lt10867_z function| lt10867_wa function| lt10867_s function| lt10867_A function| lt10867_B function| lt10867_xa function| lt10867_ya function| lt10867_za function| lt10867_C function| lt10867_Aa function| lt10867_Ba function| lt10867_D function| lt10867_E function| lt10867_Ca function| lt10867_F function| lt10867_G function| lt10867_H function| lt10867_J function| lt10867_Da function| lt10867_K function| lt10867_Ea function| lt10867_L function| lt10867_I function| lt10867_Fa function| lt10867_Ga function| lt10867_Ha function| lt10867_Ia function| lt10867_Ja function| lt10867_M function| lt10867_Ka function| lt10867_La function| lt10867_Ma function| lt10867_Na function| lt10867_Oa function| lt10867_Pa function| lt10867_N function| lt10867_Ra function| lt10867_Sa function| lt10867_Ta function| lt10867_Ua function| lt10867_Va function| lt10867_Wa function| lt10867_Xa function| lt10867_Ya function| lt10867_Za function| lt10867__a function| lt10867_0a function| lt10867_1a function| lt10867_O function| lt10867_P function| lt10867_2a function| lt10867_Q function| lt10867_R function| lt10867_3a function| lt10867_4a function| lt10867_5a function| lt10867_S function| lt10867_T function| lt10867_U function| lt10867_V function| lt10867_W function| lt10867_9a function| lt10867_6a function| lt10867_$a function| lt10867_8a function| lt10867_7a function| lt10867_X function| lt10867_bb function| lt10867_cb function| lt10867_ab function| lt10867_db function| lt10867_Z function| lt10867_gb function| lt10867_ib function| lt10867_hb function| lt10867_kb function| lt10867_fb function| lt10867_eb function| lt10867_Y function| lt10867_jb function| lt10867_2 function| lt10867_nb function| lt10867_pb function| lt10867_qb function| lt10867__ function| lt10867_ob function| lt10867_3 function| lt10867_0 function| lt10867_1 function| lt10867_lb function| lt10867_mb function| lt10867_rb function| lt10867_sb function| lt10867_wb function| lt10867_tb function| lt10867_ub function| lt10867_vb function| lt10867_xb function| lt10867_zb function| lt10867_yb function| lt10867_Ab function| lt10867_Bb function| lt10867_Cb function| lt10867_Db function| lt10867_4 function| lt10867_5 function| lt10867_Eb function| lt10867_Fb function| lt10867_Gb function| lt10867_Hb function| lt10867_Ib function| lt10867_Jb function| lt10867_Kb function| lt10867_Lb function| lt10867_Mb function| lt10867_Nb function| lt10867_7 function| lt10867_Qb function| lt10867_Rb function| lt10867_Pb function| lt10867_Ob function| lt10867_Tb function| lt10867_Sb function| lt10867_Vb function| lt10867_Ub function| lt10867_Wb function| lt10867_Xb function| lt10867_Yb function| lt10867_Zb function| lt10867__b function| lt10867_0b function| lt10867_2b function| lt10867_5b function| lt10867_4b function| lt10867_1b function| lt10867_8b function| lt10867_3b function| lt10867_6b function| lt10867_$b function| lt10867_9b function| lt10867_ac function| lt10867_7b function| lt10867_bc function| lt10867_cc function| lt10867_dc function| lt10867_8 function| lt10867_ec function| lt10867_fc function| lt10867_gc function| lt10867_hc function| lt10867_ic function| lt10867_9 function| lt10867_jc function| lt10867_kc function| lt10867_lc function| lt10867_mc function| lt10867_nc function| lt10867_oc function| lt10867_pc function| lt10867_$ function| lt10867_qc function| lt10867_tc function| lt10867_sc function| lt10867_uc function| lt10867_rc string| moengage_object object| t function| q object| f object| h string| k object| Moengage string| urlParameter object| regEx function| delete_cookie object| iframe object| body object| liveChatIframe string| appsflyerDeeplinkTarget function| closePopup boolean| __vite_is_modern_browser function| postscribe object| google_tag_manager_external string| TiktokAnalyticsObject object| ttq string| ceUserDataUrl object| parsedUserDataUrl boolean| CE_USER_SCRIPT string| CE_USER_SITE_DATA_URL string| CE_USER_DATA_URL object| twttr string| CE_USER_COMMON_SCRIPT_URL string| CE_USER_THIRDPARTY_SCRIPT_URL string| CE_USER_REMOTE_SCRIPT_URL string| CE_USER_REMOTE_HOST_URL string| chuknuStrURL object| osThankYouPageResp string| _sokClient number| osAdd2cartCount number| osCheckoutCount number| osQuickAdd2cartCount object| sokrati object| _sokParams object| _osChuknu object| _sokadd2cart_34369 object| _sokViewCategory_1106004 object| _sokHomePage object| _sokRevieworder_1106002 object| paramList function| _osViewCategory function| _osViewProduct function| _osAdd2Cart function| _osViewCart function| _osCheckout function| _osSaleComplete function| _osClick function| _osAdImpression function| _osAdClick function| renderads boolean| _OS_C string| protocol object| _sokChuknu function| _osFetchProducts object| __cfBeacon string| Flixstartturl object| inpcontainer function| flixModalFocus string| value function| _slicedToArray function| _nonIterableRest function| _unsupportedIterableToArray function| _arrayLikeToArray function| _iterableToArrayLimit function| _arrayWithHoles function| moeOnsite object| MoeOsm object| flixdelegate boolean| comparecheck

24 Cookies Go Pro

Only in urlscan Pro

Review, search, and pivot on browser cookies and persistence site data to see how a site tracks users and keeps sessions alive across visits.
Click for more information
Free trials of urlscan Pro are available.

Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.

Domain/Path Expires Name / Value
.www.blibli.com/ 1970-01-21
17:35:51
Name: __cf_bm
Value: no7MGq78sTlLbcV8prCdnGGA7ELQ0zAgYW4d51BUe.o-1791349207.3784406-1.0.1.1-t9RXWZiH43X4vKb0uQtKmP0T3iXUDAD1p35pQZGGZCl_fN8yJW4ZqS4XZzScpl7mEqotSl4CdcmnxaSJKNPGp7pQEMNAVHUPy0alerka8LWc5NZyt_Styui1mswsQKcC
.doubleclick.net/ 1970-01-22
02:57:25
Name: IDE
Value: AHWqTUmqQXg5OdJA6dAqEOdwaLu2ThO-yEMED4L0MsyXxO7sPDDK_pT4fHKObdP1
.t.co/ 1970-01-22
03:11:49
Name: muc_ads
Value: d66d1325-0923-4d63-928b-7237f79454cb
.t.co/ 1970-01-21
17:35:51
Name: __cf_bm
Value: o5HGWWhTxgIMNeVR3Z4wmdVAmc97cfzfUcoy936rUY8-1791349208.0271783-1.0.1.1-rDOZ3F0imcIkpQrTw7enzFrIppeuoy8jrylPMIYOEB1oqt0PSQ_2qIYVNsitrrzWKcvtwR_UaG5k8MlunWW8IWZ.8h3_Q4W40AQaMlj2DMI3RHRPcjmh4lIljE_7ra5J
.twitter.com/ 1970-01-22
03:11:49
Name: guest_id_marketing
Value: v1%3A179134920810433869
.twitter.com/ 1970-01-22
03:11:49
Name: guest_id_ads
Value: v1%3A179134920810433869
.twitter.com/ 1970-01-22
03:11:49
Name: personalization_id
Value: "v1_GHNNSYmEmjjlQKQw+aKdMg=="
.twitter.com/ 1970-01-22
03:11:49
Name: guest_id
Value: v1%3A179134920810433869
.twitter.com/ 1970-01-21
17:35:51
Name: __cf_bm
Value: KGaKhABBAxaUSSy16AEJzmb3QU8IGoKcfak107YGPk8-1791349208.0362043-1.0.1.1-j_5l6cL45MsQoGRjMAaS.nkFdUnhlwa3k52vN0ZnmSl8GaIM_mJ4u3zcod1K1amXOIA8DcNtDJNLadqWzxnRa2TpaAo9nLFoRqf9dcJCDwWRKrJi_MIK2wBIRQ2.FRwz
.daftarslotterpercayaidn.com/ 1970-01-22
03:11:49
Name: _ga_SF0EQEXKPW
Value: GS2.1.s1791349208$o1$g0$t1791349208$j60$l0$h0
.daftarslotterpercayaidn.com/ 1970-01-22
03:11:49
Name: _ga
Value: GA1.1.501682970.1791349208
.daftarslotterpercayaidn.com/ 1970-01-21
19:45:25
Name: _gcl_au
Value: 1.1.677347693.1791349208
.daftarslotterpercayaidn.com/ 1970-01-22
02:57:25
Name: _twsid
Value: 1791349208575-286052253.1.1791349208575
.daftarslotterpercayaidn.com/ 1970-01-22
02:57:25
Name: _twpid
Value: tw.1791349208575.807347861613528788
.tiktok.com/ 1970-01-21
19:45:25
Name: _ttp
Value: 3KLuXPKDff6x0pGg3wWSanN4ivF.1791349208736
.daftarslotterpercayaidn.com/ 1970-01-21
19:45:25
Name: _fbp
Value: fb.1.1791349208901.2022916195971342
.daftarslotterpercayaidn.com/ 1970-01-21
19:45:25
Name: _tt_enable_cookie
Value: 1
.daftarslotterpercayaidn.com/ 1970-01-21
19:45:25
Name: _ttp
Value: 01M4ABQDYHD9Q52S6H76CH23VT_.tt.1.1791349209041
.creativecdn.com/ 1970-01-22
02:21:25
Name: ts
Value: 1791349209
.daftarslotterpercayaidn.com/ 1970-01-21
19:45:25
Name: ttcsid
Value: 1791349209047::xZ1AC2rngcluDterwZ-k.1.1791349209300.0::1.-2703.0::0.0.0.0::0.0.0
.daftarslotterpercayaidn.com/ 1970-01-21
19:45:25
Name: ttcsid_C38OU43TAIRUEDS4L1L0
Value: 1791349209047::520kAe7eOhU88P_3jn8b.1.1791349209301.0
.creativecdn.com/ 1970-01-22
02:21:25
Name: g
Value: G1yBbb9MKzQvVKDCS0Oe_1791349209498
.creativecdn.com/ 1970-01-22
02:21:25
Name: c
Value: G1yBbb9MKzQvVKDCS0Oe_FAOiA95ZI30AXifJGDUt_1791349209498
.daftarslotterpercayaidn.com/ 1970-01-22
03:11:49
Name: moe_uuid
Value: 55c947f7-9133-43f8-88b6-0e142b0c732e

50 Console Messages

A page may trigger messages to the console to be logged. These are often error messages about being unable to load a resource or execute a piece of JavaScript. Sometimes they also provide insight into the technology behind a website.

Source Level URL
Text
network error URL: https://www.blibli.com/backend/content/thematic/thematic_configuration_non_canary.js
Message:
Failed to load resource: net::ERR_BLOCKED_BY_RESPONSE.NotSameOrigin
network error URL: https://www.blibli.com/bwa/2.4.5-0/index.js
Message:
Failed to load resource: net::ERR_BLOCKED_BY_RESPONSE.NotSameOrigin
network error URL: https://daftarslotterpercayaidn.com/sw/companion/v1/companion.js
Message:
Failed to load resource: the server responded with a status of 404 ()
javascript error URL: https://daftarslotterpercayaidn.com/(Line 3553)
Message:
Access to script at 'https://www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/js/summary-mixin.js' from origin 'https://daftarslotterpercayaidn.com' has been blocked by CORS policy: No 'Access-Control-Allow-Origin' header is present on the requested resource.
network error URL: https://www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/js/summary-mixin.js
Message:
Failed to load resource: net::ERR_FAILED
javascript error URL: https://daftarslotterpercayaidn.com/(Line 3553)
Message:
Access to font at 'https://www.static-src.com/frontend/static/fonts/blibli-medium-eee84661.woff2' from origin 'https://daftarslotterpercayaidn.com' has been blocked by CORS policy: The 'Access-Control-Allow-Origin' header has a value 'https://www.blibli.com' that is not equal to the supplied origin.
network error URL: https://www.static-src.com/frontend/static/fonts/blibli-medium-eee84661.woff2
Message:
Failed to load resource: net::ERR_FAILED
javascript error URL: https://daftarslotterpercayaidn.com/(Line 3553)
Message:
Access to font at 'https://www.static-src.com/frontend/static/fonts/blibli-demi-bold-6dd433a2.woff2' from origin 'https://daftarslotterpercayaidn.com' has been blocked by CORS policy: The 'Access-Control-Allow-Origin' header has a value 'https://www.blibli.com' that is not equal to the supplied origin.
network error URL: https://www.static-src.com/frontend/static/fonts/blibli-demi-bold-6dd433a2.woff2
Message:
Failed to load resource: net::ERR_FAILED
other warning URL: https://daftarslotterpercayaidn.com/(Line 3686)
Message:
Unrecognized feature: 'join-ad-interest-group'.
javascript error URL: https://daftarslotterpercayaidn.com/
Message:
Access to script at 'https://www.static-src.com/frontend/static/js/BlibliRouter.a4a077a8.js' from origin 'https://daftarslotterpercayaidn.com' has been blocked by CORS policy: The 'Access-Control-Allow-Origin' header has a value 'https://www.blibli.com' that is not equal to the supplied origin.
network error URL: https://www.static-src.com/frontend/static/js/BlibliRouter.a4a077a8.js
Message:
Failed to load resource: net::ERR_FAILED
javascript error URL: https://daftarslotterpercayaidn.com/
Message:
Access to script at 'https://www.static-src.com/frontend/static/js/customer-location-mixin.dd72e66a.js' from origin 'https://daftarslotterpercayaidn.com' has been blocked by CORS policy: The 'Access-Control-Allow-Origin' header has a value 'https://www.blibli.com' that is not equal to the supplied origin.
network error URL: https://www.static-src.com/frontend/static/js/customer-location-mixin.dd72e66a.js
Message:
Failed to load resource: net::ERR_FAILED
javascript error URL: https://daftarslotterpercayaidn.com/
Message:
Access to script at 'https://www.static-src.com/frontend/static/js/FootSection.709acb56.js' from origin 'https://daftarslotterpercayaidn.com' has been blocked by CORS policy: The 'Access-Control-Allow-Origin' header has a value 'https://www.blibli.com' that is not equal to the supplied origin.
network error URL: https://www.static-src.com/frontend/static/js/FootSection.709acb56.js
Message:
Failed to load resource: net::ERR_FAILED
javascript error URL: https://daftarslotterpercayaidn.com/
Message:
Access to script at 'https://www.static-src.com/frontend/static/js/AccordionContent.6cf8e4dd.js' from origin 'https://daftarslotterpercayaidn.com' has been blocked by CORS policy: The 'Access-Control-Allow-Origin' header has a value 'https://www.blibli.com' that is not equal to the supplied origin.
network error URL: https://www.static-src.com/frontend/static/js/AccordionContent.6cf8e4dd.js
Message:
Failed to load resource: net::ERR_FAILED
javascript error URL: https://daftarslotterpercayaidn.com/
Message:
Access to script at 'https://www.static-src.com/frontend/static/js/index.5457813a.js' from origin 'https://daftarslotterpercayaidn.com' has been blocked by CORS policy: The 'Access-Control-Allow-Origin' header has a value 'https://www.blibli.com' that is not equal to the supplied origin.
network error URL: https://www.static-src.com/frontend/static/js/index.5457813a.js
Message:
Failed to load resource: net::ERR_FAILED
javascript error URL: https://daftarslotterpercayaidn.com/
Message:
Access to script at 'https://www.static-src.com/frontend/static/js/Location.c79a4a93.js' from origin 'https://daftarslotterpercayaidn.com' has been blocked by CORS policy: The 'Access-Control-Allow-Origin' header has a value 'https://www.blibli.com' that is not equal to the supplied origin.
network error URL: https://www.static-src.com/frontend/static/js/Location.c79a4a93.js
Message:
Failed to load resource: net::ERR_FAILED
javascript error URL: https://daftarslotterpercayaidn.com/
Message:
Access to script at 'https://www.static-src.com/frontend/static/js/CustomerLocation.49933ea8.js' from origin 'https://daftarslotterpercayaidn.com' has been blocked by CORS policy: The 'Access-Control-Allow-Origin' header has a value 'https://www.blibli.com' that is not equal to the supplied origin.
network error URL: https://www.static-src.com/frontend/static/js/CustomerLocation.49933ea8.js
Message:
Failed to load resource: net::ERR_FAILED
javascript error URL: https://daftarslotterpercayaidn.com/
Message:
Access to script at 'https://www.static-src.com/frontend/static/js/FooterDetail.22d2666a.js' from origin 'https://daftarslotterpercayaidn.com' has been blocked by CORS policy: The 'Access-Control-Allow-Origin' header has a value 'https://www.blibli.com' that is not equal to the supplied origin.
network error URL: https://www.static-src.com/frontend/static/js/FooterDetail.22d2666a.js
Message:
Failed to load resource: net::ERR_FAILED
javascript error URL: https://daftarslotterpercayaidn.com/
Message:
Access to script at 'https://www.static-src.com/frontend/static/js/LazyImage.92de27af.js' from origin 'https://daftarslotterpercayaidn.com' has been blocked by CORS policy: The 'Access-Control-Allow-Origin' header has a value 'https://www.blibli.com' that is not equal to the supplied origin.
network error URL: https://www.static-src.com/frontend/static/js/LazyImage.92de27af.js
Message:
Failed to load resource: net::ERR_FAILED
javascript error URL: https://daftarslotterpercayaidn.com/
Message:
Access to script at 'https://www.static-src.com/frontend/static/js/address-event.0a54fb2b.js' from origin 'https://daftarslotterpercayaidn.com' has been blocked by CORS policy: The 'Access-Control-Allow-Origin' header has a value 'https://www.blibli.com' that is not equal to the supplied origin.
network error URL: https://www.static-src.com/frontend/static/js/address-event.0a54fb2b.js
Message:
Failed to load resource: net::ERR_FAILED
network error URL: https://td.doubleclick.net/td/rul/880395410?random=1726498671571&cv=11&fst=1726498671571&fmt=3&bg=ffffff&guid=ON&async=1&gtm=45je4990v877689920z8810058345za200zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FmetaData%3D4eHyfurj4yL7Q4Ucv84uGYHJb0g2t%2BFdwECMb3QsHNjtAqmaWkaBfGgt5w9qTEikAP03CsR8aLRQodyhRwzA9w%3D%3D%26pickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Online%20Mall%20Blibli.com%2C%20Sensasi%20Belanja%20Online%20Shop%20ala%20Mall&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=event%3Dgtag.config
Message:
Failed to load resource: the server responded with a status of 404 ()
network error URL: https://td.doubleclick.net/td/rul/925089264?random=1726498714047&cv=11&fst=1726498714047&fmt=3&bg=ffffff&guid=ON&async=1&gtm=45be4990z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1024&u_h=824&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=ecomm_pagetype%3Dproduct%3Becomm_prodid%3DNUT-60023-01292%3Becomm_totalvalue%3D343900
Message:
Failed to load resource: the server responded with a status of 404 ()
network error URL: https://td.doubleclick.net/td/rul/880395410?random=1726498673589&cv=11&fst=1726498673589&fmt=3&bg=ffffff&guid=ON&async=1&gtm=45be4990v877689920z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&label=hEx3CKjo-eADEJKJ56MD&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&value=0&bttype=purchase&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&capi=1&ct_cookie_present=0
Message:
Failed to load resource: the server responded with a status of 404 ()
network error URL: https://td.doubleclick.net/td/rul/920334631?random=1726498673536&cv=11&fst=1726498673536&fmt=3&bg=ffffff&guid=ON&async=1&gtm=45be4990z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=ecomm_pagetype%3Dretail-product-detail%3Becomm_prodid%3DNUT-60023-01292%3Becomm_totalvalue%3D343900
Message:
Failed to load resource: the server responded with a status of 404 ()
network error URL: https://td.doubleclick.net/td/rul/920334631?random=1726498714059&cv=11&fst=1726498714059&fmt=3&bg=ffffff&guid=ON&async=1&gtm=45be4990z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1024&u_h=824&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=ecomm_pagetype%3Dretail-product-detail%3Becomm_prodid%3DNUT-60023-01292%3Becomm_totalvalue%3D343900
Message:
Failed to load resource: the server responded with a status of 404 ()
network error URL: https://td.doubleclick.net/td/rul/925089264?random=1726498673524&cv=11&fst=1726498673524&fmt=3&bg=ffffff&guid=ON&async=1&gtm=45be4990z8810058345za201zb810058345&gcd=13l3l3l3l1l1&dma=0&tag_exp=0&u_w=1920&u_h=1080&url=https%3A%2F%2Fwww.blibli.com%2Fp%2Ftwin-pack-tropicana-slim-beras-porang-instan-1000-g%2Fis--NUT-60023-01292-00001%3FpickupPointCode%3DPP-3495802&ref=https%3A%2F%2Fwww.blibli.com%2Fflashsale%3Fsku%3DALS-60310-00048%26page%3D1&hn=www.googleadservices.com&frm=0&tiba=Promo%20Twin%20Pack-%20Tropicana%20Slim%20Beras%20Porang%20Instan%201000%20G%20Diskon%2018%25%20Di%20Seller%20Nutrifood%20Official%20Store%20-%20Pisangan%20Timur%2C%20Kota%20Jakarta%20Timur%20%7C%20Blibli&npa=0&pscdl=noapi&auid=426120352.1726498660&uaa=x86&uab=64&uafvl=Chromium%3B128.0.6613.138%7CNot%253BA%253DBrand%3B24.0.0.0%7CGoogle%2520Chrome%3B128.0.6613.138&uamb=0&uam=&uap=Windows&uapv=15.0.0&uaw=0&fledge=1&data=ecomm_pagetype%3Dproduct%3Becomm_prodid%3DNUT-60023-01292%3Becomm_totalvalue%3D343900
Message:
Failed to load resource: the server responded with a status of 404 ()
network error URL: https://t.o-s.io/site?res=1600x1200&lang=pl&client_id=115069&product_category=default&item_identifier=%3CITEM%20ID%3E&_ur=41034427&_ref=
Message:
Failed to load resource: the server responded with a status of 503 ()
network error URL: https://daftarslotterpercayaidn.com/cdn-cgi/rum?
Message:
Failed to load resource: the server responded with a status of 404 ()
network error
Message:
A bad HTTP response code (404) was received when fetching the script.
network error
Message:
A bad HTTP response code (404) was received when fetching the script.
javascript warning URL: https://daftarslotterpercayaidn.com/
Message:
The resource https://www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/js/product-id-mixin.js was preloaded using link preload but not used within a few seconds from the window's load event. Please make sure it has an appropriate `as` value and it is preloaded intentionally.
javascript warning URL: https://daftarslotterpercayaidn.com/
Message:
The resource https://www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/js/summary-mixin.js was preloaded using link preload but not used within a few seconds from the window's load event. Please make sure it has an appropriate `as` value and it is preloaded intentionally.
javascript warning URL: https://daftarslotterpercayaidn.com/
Message:
The resource https://www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/js/DetailPage.js was preloaded using link preload but not used within a few seconds from the window's load event. Please make sure it has an appropriate `as` value and it is preloaded intentionally.
javascript warning URL: https://daftarslotterpercayaidn.com/
Message:
The resource https://www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/js/GatewayPage.js was preloaded using link preload but not used within a few seconds from the window's load event. Please make sure it has an appropriate `as` value and it is preloaded intentionally.
javascript warning URL: https://daftarslotterpercayaidn.com/
Message:
The resource https://www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/js/referrer-mixin.js was preloaded using link preload but not used within a few seconds from the window's load event. Please make sure it has an appropriate `as` value and it is preloaded intentionally.
javascript warning URL: https://daftarslotterpercayaidn.com/
Message:
The resource https://www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/js/product-id-mixin.js was preloaded using link preload but not used within a few seconds from the window's load event. Please make sure it has an appropriate `as` value and it is preloaded intentionally.
javascript warning URL: https://daftarslotterpercayaidn.com/
Message:
The resource https://www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/js/summary-mixin.js was preloaded using link preload but not used within a few seconds from the window's load event. Please make sure it has an appropriate `as` value and it is preloaded intentionally.
javascript warning URL: https://daftarslotterpercayaidn.com/
Message:
The resource https://www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/js/DetailPage.js was preloaded using link preload but not used within a few seconds from the window's load event. Please make sure it has an appropriate `as` value and it is preloaded intentionally.
javascript warning URL: https://daftarslotterpercayaidn.com/
Message:
The resource https://www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/js/GatewayPage.js was preloaded using link preload but not used within a few seconds from the window's load event. Please make sure it has an appropriate `as` value and it is preloaded intentionally.
javascript warning URL: https://daftarslotterpercayaidn.com/
Message:
The resource https://www.static-src.com/frontend/product-detail/static/2.26.0-1/desktop/js/referrer-mixin.js was preloaded using link preload but not used within a few seconds from the window's load event. Please make sure it has an appropriate `as` value and it is preloaded intentionally.

Indicators

This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.

ad.doubleclick.net
analytics-ipv6.tiktokw.us
analytics.tiktok.com
analytics.twitter.com
asia.creativecdn.com
blibli.api.useinsider.com
c.o-s.io
cdn.moengage.com
connect.facebook.net
daftarslotterpercayaidn.com
dev.visualwebsiteoptimizer.com
dv-c3e594c6d429469e90b54478358619c3.ecs.us-east-1.on.aws
gen.blackmolesamp.com
googleads.g.doubleclick.net
i.ibb.co.com
media.flixcar.com
media.flixfacts.com
meubelkayumurah.pics
prod.flixgvid.flix360.io
region1.google-analytics.com
rt.flix360.com
script.crazyegg.com
sdk-01.moengage.com
static.ads-twitter.com
static.cloudflareinsights.com
t.co
t.o-s.io
tags.crwdcntrl.net
td.doubleclick.net
utt.impactcdn.com
websdk.appsflyer.com
www.blibli.com
www.facebook.com
www.google-analytics.com
www.google.com
www.google.pl
www.googleadservices.com
www.googletagmanager.com
www.static-src.com
www.blibli.com
www.static-src.com
103.132.192.30
104.16.80.73
104.19.147.8
108.138.26.69
142.251.110.94
142.251.127.149
142.251.13.154
142.251.14.157
142.251.156.119
142.251.157.119
146.75.120.157
162.159.133.61
172.66.0.227
172.67.155.237
178.128.116.123
18.64.211.102
18.64.211.128
18.66.102.77
18.66.122.124
18.66.147.45
188.114.97.3
192.178.183.97
2.16.10.92
216.239.32.178
216.239.34.36
3.161.82.109
3.161.82.25
34.107.218.251
34.117.1.79
34.193.159.151
35.186.249.72
35.244.195.172
45.43.142.8
57.144.244.1
57.144.244.128
63.34.183.36
92.123.104.175
0acbc669c7d0ad6ebea3858b6c1c6ee2fd335ec89dedb84d14190d0c12c85be2
10114649a2879814546a925ec8e98c011fae099aa68d45f864ba9c07467da14e
10f3cb8013466a17604698d4c6d662f8ba065d3bab865b519d79490ba0e91b5b
14791f324ed7deef8506110328b41d3f00c75fb5bf433a798a98ebbee36d3c53
1877334064592aa3d57f28dd4eef88800dd67d81c5654e2520de1107cad36932
2fa614ac18e2af5676a7bc9cebb918990484ebf124765a96c5fdfb9de8ff5a24
3064c443efe71ba06a3aa0a60a29fb67ed9b49a55597a61b2f23eb345567ffb3
3433dacfefe0557bcee1f621a276ecfea38a3fc6f5005c06d8186f28000d15d7
38cc5a6ce8c996a8b2885078031b76590e479c2dfc357f02909eb7b5c3433624
408b20965467395fee579a2f356e3f37d3a2bb00078d3af0174f46aae1b52548
417c2fa4ff8cf5e36b1797c558e99b797cf8e9a960ce8e126ccd8de6ff09efca
4b77eae349a8cbcea7133cf3640a64ebf1f69d54d8f6469d7be6fdc188ca4ca4
4f41ece4a8b3a961b00908c362d7474dda8cde93ff6f39976454b7137a5ffedd
543a2bc3bdebec6bc98871c2f227d07e725618df26154df87e5504b1d73f2c63
566134ecec9a65a92f3b48b95e8227974a09fefa7a985a57d58f731da5249f99
5754889f70f64e2822a0630a8416d0292e00014297d8d585fdcb39bd8e977a03
597e9639dbadba00680015f321c3b4acfcbe8cb47f0e61420dcae4d09e391af8
5c4ff6f1f404bf857f698d88077aa607d3c1efb125748e69932584aa0596704a
5f2badb55c07c25d970b453e5650df9ce4e86a6ca5b6f8a96f7041b73b9210ba
66ab1cdce2c0f27f6127b7da1d318aeb7994d650f78080aff1f969ec515aa3d1
6b9039b8c10a3fcac130a6e154fa127cd40f039e7b58abe6200f1925e4bc625b
6dd433a2e6f5626e3a794f2bd1688efb5bb59cdbae73d8b224d773875422a6d2
6e9d1c8da726584f12acb23c3345d00715a7e08476b834b8694301b51f3ebec0
751f56579ad314549bd872256cbb7c3e483630c7da99b03fe324175a242c36c2
7701282ea59743a1d336ee5ede4e6805ca9572c28ad013fa956fb39f18de0d69
783b18e86fc50a89ad8b683a1a7f61ee77da33e169b0c674d11f712c1d863917
7992b83823c161d3447d6fc3aaa10be33267de183d2d1120e7301720fc8b0ce0
79bc978bffc509c0407154ae6e97676b93c84996cedbbc5a06cd4a34de052721
7a7de1c15385fc9deab903e092b05599fc18558b914e80394cf7c1ea46b2fdf3
7ac9c58532de36879ea6d7d357f8878e16a18bff367f898fb7db398a9ae643c5
7ad1d4cb7d63f41b6ccd3444a64a5b753e777aa0aa101df63875fe59362d423c
7bdc38dabd16b72f068e78906e2ab7374ff0525a29a8855d8e3a5fbb7901a21d
7c008ff0e64ce1d8797d6afe11420b8d24ea4036f7ef1fc115575027e53ee132
80e1acedc648d6d06f06342e0db58dbd7f965c569da8f80aa3f0bfb29247e6d2
8337212354871836e6763a41e615916c89bac5b3f1f0adf60ba43c7c806e1015
855fd1491666c31b8b181330a959ce2fed48235696368901f7d8488bd53eb5bf
86406a30f04aa2e75cf60409fe44ab1b557b827d3ae413d68164cdc82ecb9082
8968e2907b8936778ed050dd55d8ef7232b3d32ee95b1f7122b4dfa9e22c4839
89a2a82574d35ba44820a985fff208cb50bbe810307f7ee069f97fd391c9a131
8bdc0627259cf14bdcf48d3351710ab6c23ad23289427e977a1d9df48ee62793
8d6b712cd54b8b0c809ed2daa5b35913f5fb92fdb2e643b0e754227068d0f088
8e29c2c9cca933ffa27caf938488369160297167cf9486ec955bb99bc1cd1182
980ed2ca9a1e43c42e0d94a927fc79f3e07c62d0b9623501a2b8015d04948222
985fa323ed22e810b311c5d7032cbef87f2a377ee0b217b8d13a544cf034c3ef
9d6b9d47e1ec88f46c7a91dc602a947e3500e0cfc3c4df0d9faeb24d2dde3925
9f8234eecfdf4dd0cd9783e71222389c7aa2c8382a00c42f4e0326a43e6db96f
a137e0772b72a2f40d633cd0767f0f8b0d2fb8582a1d88b198d6a08e95a84e3a
a31a2cbca80845eb52a64aac7d169d1ed00b9d9770598d565f410ecf2f0fbe4f
a4e043f37b5980394b4c7d6f3d55edecb9390249aa2f4de55a082a1bdfd27164
a6ef5940d1656af10f49676a33d6dda462853547fa97e9b0231c7d7339cfde3f
a8784ee846c1266bed7cab511a9814e89273945fdfae2cadf0dc26c4cf97c601
aa03dc59bdca72631d2301e4297cfa030bd31b907dc138e7b973d12311c90a22
aab6a662df923c04739f37c6a6d7f13fb91c8e3c6addd82fd5a6959e6f6241fb
ac8778041fdb7f2e08ceb574c9a766247ea26f1a7d90fa854c4efcf4b361a957
aca73fc574e12740e3368860b88a284d01b643456f3ed6a06322ecb47750563f
adaddbdb405b4cb59988b54dd6e446f5b0c3359f87d4536f567b2d36dd60aefc
b0cebe7498636dd05d4a71ebc19036a630a90607694717ba4f96e163dcddadc0
b1ef57f4628064809f0a4d068614c1effab4701076121c3d23d2cca45b9cede3
b24be3f1a44e12d12428e08feb1f043434035af652507659715dd944d26c3262
ba0b7eb3715835052d209004edb5678fb16783f5cbb27214e581570c4124ff92
bd15337dca5ab822c0f983145a7428b0449b5387de2104f7a5a3c6bb4348767f
bf3f4f2ee6a19afb6e25e733a283990dcbdbbdd9ab1d6bb4dcd1e2962065a07a
bf7f8eafeefe4b116ebd7e3e2b82f077e749b186f1605b3ca86c647ecbc6ed6c
c12c4ba7cfe24b418c778165afe99eb5193265d2403e440531d3f61887ff0a5c
c5007d87986fb629a4bc65de165f596febfbe3c2f0e65a88f5a75a1092b4e7e7
cad998d3504e0f3dd554c65cc4362db2db12b0a46d4aee2b9a9eee75720a9d30
cb42c57757d45d43019fde11ca7964ff5ce63026c2e3d25f29586a7bba20e1d7
cca7772f89154d90db384f90e3ea0cfa81ea4b891fa3ba6da177f8d43349b01a
cce72e79b42c4436f8bae6d1ec8c6e8b08049a7cab38863cba3bb29925f44785
cf44b1cf8d9d8d9f553d8d66bacd621fbedf51aa2c933360e26ff12aa2673457
d3e7edc241acef61b4e3d9169d95bbecd423c250fde643b663b661b52d3cc3e3
d45a5c3d6cfa97ac248077fdfdece56c05f88e3b02ba06175cd2696cfaa6f653
d66dd0f2f24c4343661a5396e1ba76782fe651f7d422209eded956ebf90900fc
dbef5e5530003b7233e944856c23d1437902a2d3568cdfd2beaf2166e9ca9139
dbfaa41c979bbb839f78a4470b0a0e119262c06390e95d48e13ffd5c994ce1f1
e1ac4849b9d4a498b68f8aca01e6ed99a11d94b35a2cec533b3916b8fb722fd6
e2c6fdea2cb55187591f6713804205d250f8f36cec70bdfb74b247f0181936f5
e2f36a32e1ba4787a3391b7a670fa43a9bec7431f4823774344b68c398eed905
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
e7368a0cfada6443baf2b3ae47db15ff08df634ea10b2bebd0a5c5fe8e37b3f0
eee84661a5d29de16948e34abed935317718666412654a2a0fd753b0db7c6971
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
f1a61277e3f902f50ab42015d8b07218db9b7601bb0967e54a52bfdcb4fa7e81
f3f4ed6781c8e5f84b5a472f9a594dca8c065eed09eb5f2cc7377e7f0ff10556