
www.paycom.com
107.162.254.104
Public Scan
Open in
urlscan Pro
http://test-app.rpspayroll.org/ 6mo old
Effective URL:
https://www.paycom.com/ 10yr old
Submission: On October 07 via api (October 7th 2026, 8:22:15 am UTC) from US — Scanned from US Go Pro
Only in urlscan Pro
- Select different country locations for Private Scans.
- Use a global network of additional scanning locations and residential IPs for scanning.
- Interact with pages while you are scanning them.
- Download files from remote websites.
- Scan websites on the Tor Network.
Summary
TLS certificate: Issued by DigiCert Global G2 TLS RSA SHA256 202... on April 30th 2026. Valid for: 7mo.
This is the only time www.paycom.com was scanned on urlscan.io!
urlscan.io Verdict: No classification
Domain & IP information
| IP Address | AS Autonomous System | ||
|---|---|---|---|
| 1 1 | 216.226.2.26 216.226.2.26 | 397497 (PAYCOM) (PAYCOM - Paycom Payroll) | |
| 1 54 | 107.162.254.104 107.162.254.104 | 35280 (F5 F5 Net...) (F5 F5 Networks SARL) | |
| 10 | 104.18.87.42 104.18.87.42 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 5 | 23.49.248.11 23.49.248.11 | 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.) | |
| 2 8 | 151.101.65.181 151.101.65.181 | 54113 (FASTLY) (FASTLY - Fastly) | |
| 2 | 13.33.67.105 13.33.67.105 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 4 | 142.250.191.8 142.250.191.8 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 104.18.32.137 104.18.32.137 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 104.17.207.5 104.17.207.5 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 146.75.28.157 146.75.28.157 | 54113 (FASTLY) (FASTLY - Fastly) | |
| 6 | 150.171.28.10 150.171.28.10 | 8075 (MICROSOFT...) (MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation) | |
| 2 | 23.200.3.22 23.200.3.22 | 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.) | |
| 2 | 23.13.173.12 23.13.173.12 | 16625 (AKAMAI-AS) (AKAMAI-AS - Akamai Technologies) | |
| 1 | 13.32.241.20 13.32.241.20 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 1 | 104.18.30.176 104.18.30.176 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 9 | 23.40.18.49 23.40.18.49 | 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.) | |
| 2 | 57.144.180.128 57.144.180.128 | 32934 (FACEBOOK) (FACEBOOK - Facebook) | |
| 3 | 104.18.37.212 104.18.37.212 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 5 | 142.251.153.119 142.251.153.119 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 2 3 | 142.251.45.198 142.251.45.198 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 13.223.123.134 13.223.123.134 | 14618 (AMAZON-AES) (AMAZON-AES - Amazon.com) | |
| 1 | 13.226.103.193 13.226.103.193 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 1 | 104.19.164.102 104.19.164.102 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 142.250.68.194 142.250.68.194 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 2 10 | 3.33.220.150 3.33.220.150 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 1 | 162.159.140.229 162.159.140.229 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 172.66.0.227 172.66.0.227 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 35.170.37.64 35.170.37.64 | 14618 (AMAZON-AES) (AMAZON-AES - Amazon.com) | |
| 1 | 104.16.188.41 104.16.188.41 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 142.251.45.206 142.251.45.206 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 172.253.62.157 172.253.62.157 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 2 | 13.32.241.107 13.32.241.107 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 2 2 | 32.192.128.18 32.192.128.18 | 14618 (AMAZON-AES) (AMAZON-AES - Amazon.com) | |
| 4 4 | 68.67.160.75 68.67.160.75 | 29990 (ASN-APPNEXUS) (ASN-APPNEXUS - Xandr Inc.) | |
| 2 2 | 142.251.41.162 142.251.41.162 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 1 | 216.19.192.2 216.19.192.2 | 26667 (RUBICONPR...) (RUBICONPROJECT - Magnite) | |
| 1 | 3.228.126.156 3.228.126.156 | 14618 (AMAZON-AES) (AMAZON-AES - Amazon.com) | |
| 5 | 104.16.118.43 104.16.118.43 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 3 5 | 172.64.146.215 172.64.146.215 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 2 | 34.21.100.80 34.21.100.80 | 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC) | |
| 1 | 192.28.164.179 192.28.164.179 | 15224 (OMNITURE) (OMNITURE - Adobe Inc.) | |
| 1 | 57.144.180.1 57.144.180.1 | 32934 (FACEBOOK) (FACEBOOK - Facebook) | |
| 1 | 23.219.161.114 23.219.161.114 | 20940 (AKAMAI-AS...) (AKAMAI-ASN1 Akamai International B.V.) | |
| 1 2 | 142.250.217.134 142.250.217.134 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 142.250.65.66 142.250.65.66 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 4 | 52.223.40.198 52.223.40.198 | 16509 (AMAZON-02) (AMAZON-02 - Amazon.com) | |
| 156 | 42 |
ASN397497 (PAYCOM - Paycom Payroll, LLC, US)
| test-app.rpspayroll.org 6mo old |
ASN35280 (F5 F5 Networks SARL, FR)
| www.paycomonline.com 14yr old | |
| www.paycom.com 10yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| cdn.cookielaw.org 10yr old |
ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL)
PTR: a23-49-248-11.deploy.static.akamaitechnologies.com
| cdn.paycom.com 5yr old |
ASN54113 (FASTLY - Fastly, Inc., US)
| play.vidyard.com 13yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-13-33-67-105.jfk50.r.cloudfront.net
| cdn.vidyard.com 14yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: pnlgaa-az-in-f8.1e100.net
| www.googletagmanager.com 14yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| geolocation.onetrust.com 9yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| cdn.jsdelivr.net 14yr old |
ASN54113 (FASTLY - Fastly, Inc., US)
| static.ads-twitter.com 10yr old |
ASN8075 (MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation, US)
| bat.bing.com 13yr old |
ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL)
PTR: a23-200-3-22.deploy.static.akamaitechnologies.com
| snap.licdn.com 10yr old |
ASN16625 (AKAMAI-AS - Akamai Technologies, Inc., US)
PTR: a23-13-173-12.deploy.static.akamaitechnologies.com
| munchkin.marketo.net 10yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-13-32-241-20.jfk50.r.cloudfront.net
| js.adsrvr.org 10yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| tracking.g2crowd.com 10yr old |
ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL)
PTR: a23-40-18-49.deploy.static.akamaitechnologies.com
| analytics.tiktok.com 7yr old |
ASN32934 (FACEBOOK - Facebook, Inc., US)
PTR: xx-fbcdn-shv-03-lga3.fbcdn.net
| connect.facebook.net 14yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| js.zi-scripts.com 4yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: pnlgaa-au-in-f6.1e100.net
| ad.doubleclick.net 10yr old |
ASN14618 (AMAZON-AES - Amazon.com, Inc., US)
PTR: ec2-13-223-123-134.compute-1.amazonaws.com
| b.videoamp.com 7yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-13-226-103-193.jfk52.r.cloudfront.net
| d34r8q7sht0t9k.cloudfront.net 4yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| scout-cdn.salesloft.com 9yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: pnlgaa-ax-in-f2.1e100.net
| googleads.g.doubleclick.net 10yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: a12b7a488abeaa9e4.awsglobalaccelerator.com
| insight.adsrvr.org 10yr old | |
| match.adsrvr.org 10yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| analytics.twitter.com 10yr old |
ASN14618 (AMAZON-AES - Amazon.com, Inc., US)
PTR: ec2-35-170-37-64.compute-1.amazonaws.com
| ipv4.podscribe.com 3yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| tracking-api.g2.com 2yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: pnlgaa-au-in-f14.1e100.net
| analytics.google.com 9yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: bc-in-f157.1e100.net
| stats.g.doubleclick.net 10yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: server-13-32-241-107.jfk50.r.cloudfront.net
| js.adsrvr.org 10yr old |
ASN14618 (AMAZON-AES - Amazon.com, Inc., US)
PTR: ec2-32-192-128-18.compute-1.amazonaws.com
| dpm.demdex.net 10yr old |
ASN29990 (ASN-APPNEXUS - Xandr Inc., US)
PTR: 673.bm-nginx-loadbalancer.mgmt.nym2.adnexus.net
| ib.adnxs.com 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: lclgaa-at-in-f2.1e100.net
| cm.g.doubleclick.net 10yr old |
ASN26667 (RUBICONPROJECT - Magnite, Inc., US)
| pixel.rubiconproject.com 10yr old |
ASN14618 (AMAZON-AES - Amazon.com, Inc., US)
PTR: ec2-3-228-126-156.compute-1.amazonaws.com
| verifi.podscribe.com 5yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| ws-assets.zoominfo.com 7yr old | |
| ws.zoominfo.com 7yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| px.ads.linkedin.com 9yr old | |
| www.linkedin.com 14yr old |
ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US)
PTR: 80.100.21.34.bc.googleusercontent.com
| scout.salesloft.com 9yr old |
ASN15224 (OMNITURE - Adobe Inc., US)
| 502-gzq-487.mktoresp.com 8yr old |
ASN32934 (FACEBOOK - Facebook, Inc., US)
PTR: edge-star-mini-shv-03-lga3.facebook.com
| www.facebook.com 12yr old |
ASN20940 (AKAMAI-ASN1 Akamai International B.V., NL)
PTR: a23-219-161-114.deploy.static.akamaitechnologies.com
| analytics-ipv6.tiktokw.us 3yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: lax31s19-in-f6.1e100.net
| 15036603.fls.doubleclick.net 2yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: lclgaa-ax-in-f2.1e100.net
| adservice.google.com 9yr old |
ASN16509 (AMAZON-02 - Amazon.com, Inc., US)
PTR: a6370ebea231e0c9a.awsglobalaccelerator.com
| insight.adsrvr.org 10yr old |
| Apex Domain Subdomains |
Transfer | |
|---|---|---|
| 58 |
paycom.com
www.paycom.com — Cisco Umbrella Rank: 88199 10yr old cdn.paycom.com — Cisco Umbrella Rank: 118477 5yr old |
3 MB |
| 17 |
adsrvr.org
2 redirects
js.adsrvr.org — Cisco Umbrella Rank: 1399 10yr old insight.adsrvr.org — Cisco Umbrella Rank: 1290 10yr old match.adsrvr.org — Cisco Umbrella Rank: 495 10yr old |
23 KB |
| 10 |
vidyard.com
2 redirects
play.vidyard.com — Cisco Umbrella Rank: 7187 13yr old cdn.vidyard.com — Cisco Umbrella Rank: 18249 14yr old |
169 KB |
| 10 |
cookielaw.org
cdn.cookielaw.org — Cisco Umbrella Rank: 450 10yr old |
207 KB |
| 9 |
doubleclick.net
5 redirects
ad.doubleclick.net — Cisco Umbrella Rank: 135 10yr old googleads.g.doubleclick.net — Cisco Umbrella Rank: 66 10yr old stats.g.doubleclick.net — Cisco Umbrella Rank: 152 10yr old cm.g.doubleclick.net — Cisco Umbrella Rank: 332 10yr old 15036603.fls.doubleclick.net — Cisco Umbrella Rank: 113405 2yr old |
5 KB |
| 9 |
tiktok.com
analytics.tiktok.com — Cisco Umbrella Rank: 680 7yr old |
166 KB |
| 7 |
google.com
www.google.com — Cisco Umbrella Rank: 3 14yr old analytics.google.com — Cisco Umbrella Rank: 143 9yr old adservice.google.com — Cisco Umbrella Rank: 813 9yr old |
190 B |
| 6 |
bing.com
bat.bing.com — Cisco Umbrella Rank: 420 13yr old |
33 KB |
| 5 |
linkedin.com
3 redirects
px.ads.linkedin.com — Cisco Umbrella Rank: 362 9yr old www.linkedin.com — Cisco Umbrella Rank: 755 14yr old |
3 KB |
| 5 |
zoominfo.com
ws-assets.zoominfo.com — Cisco Umbrella Rank: 13936 7yr old ws.zoominfo.com — Cisco Umbrella Rank: 4568 7yr old |
17 KB |
| 4 |
adnxs.com
4 redirects
ib.adnxs.com — Cisco Umbrella Rank: 358 10yr old |
4 KB |
| 4 |
googletagmanager.com
www.googletagmanager.com — Cisco Umbrella Rank: 44 14yr old |
671 KB |
| 3 |
salesloft.com
scout-cdn.salesloft.com — Cisco Umbrella Rank: 14329 9yr old scout.salesloft.com — Cisco Umbrella Rank: 18306 9yr old |
4 KB |
| 3 |
zi-scripts.com
js.zi-scripts.com — Cisco Umbrella Rank: 5192 4yr old |
7 KB |
| 2 |
demdex.net
2 redirects
dpm.demdex.net — Cisco Umbrella Rank: 364 10yr old |
1 KB |
| 2 |
podscribe.com
ipv4.podscribe.com — Cisco Umbrella Rank: 8837 3yr old verifi.podscribe.com — Cisco Umbrella Rank: 7498 5yr old |
462 B |
| 2 |
facebook.net
connect.facebook.net — Cisco Umbrella Rank: 215 14yr old |
207 KB |
| 2 |
marketo.net
munchkin.marketo.net — Cisco Umbrella Rank: 4747 10yr old |
7 KB |
| 2 |
licdn.com
snap.licdn.com — Cisco Umbrella Rank: 849 10yr old |
23 KB |
| 1 |
tiktokw.us
analytics-ipv6.tiktokw.us — Cisco Umbrella Rank: 1135 3yr old |
977 B |
| 1 |
facebook.com
www.facebook.com — Cisco Umbrella Rank: 136 12yr old |
20 B |
| 1 |
mktoresp.com
502-gzq-487.mktoresp.com — Cisco Umbrella Rank: 112295 8yr old |
318 B |
| 1 |
rubiconproject.com
1 redirects
pixel.rubiconproject.com — Cisco Umbrella Rank: 576 10yr old |
2 KB |
| 1 |
g2.com
tracking-api.g2.com — Cisco Umbrella Rank: 9920 2yr old |
|
| 1 |
twitter.com
analytics.twitter.com — Cisco Umbrella Rank: 1192 10yr old |
687 B |
| 1 |
t.co
t.co — Cisco Umbrella Rank: 1212 14yr old |
668 B |
| 1 |
cloudfront.net
d34r8q7sht0t9k.cloudfront.net — Cisco Umbrella Rank: 6304 4yr old |
6 KB |
| 1 |
videoamp.com
b.videoamp.com — Cisco Umbrella Rank: 3756 7yr old |
312 B |
| 1 |
g2crowd.com
tracking.g2crowd.com — Cisco Umbrella Rank: 11432 10yr old |
2 KB |
| 1 |
ads-twitter.com
static.ads-twitter.com — Cisco Umbrella Rank: 1353 10yr old |
17 KB |
| 1 |
jsdelivr.net
cdn.jsdelivr.net — Cisco Umbrella Rank: 274 14yr old |
4 KB |
| 1 |
onetrust.com
geolocation.onetrust.com — Cisco Umbrella Rank: 782 9yr old |
285 B |
| 1 |
paycomonline.com
1 redirects
www.paycomonline.com — Cisco Umbrella Rank: 392313 14yr old |
112 B |
| 1 |
rpspayroll.org
1 redirects
test-app.rpspayroll.org 6mo old |
572 B |
| 0 |
ml-attr.com
Failed
s.ml-attr.com Failed 10yr old |
|
| 156 | 35 |
| Domain | Requested by | |
|---|---|---|
| 53 | www.paycom.com |
www.paycom.com
|
| 10 | cdn.cookielaw.org |
www.paycom.com
cdn.cookielaw.org |
| 9 | analytics.tiktok.com |
www.paycom.com
analytics.tiktok.com |
| 8 | match.adsrvr.org |
js.adsrvr.org
match.adsrvr.org |
| 8 | play.vidyard.com |
2 redirects
www.paycom.com
play.vidyard.com |
| 6 | insight.adsrvr.org |
2 redirects
js.adsrvr.org
|
| 6 | bat.bing.com |
www.googletagmanager.com
bat.bing.com |
| 5 | www.google.com |
www.googletagmanager.com
|
| 5 | cdn.paycom.com |
www.paycom.com
|
| 4 | px.ads.linkedin.com |
2 redirects
snap.licdn.com
|
| 4 | ws.zoominfo.com |
js.zi-scripts.com
ws-assets.zoominfo.com |
| 4 | ib.adnxs.com | 4 redirects |
| 4 | www.googletagmanager.com |
www.paycom.com
www.googletagmanager.com |
| 3 | ad.doubleclick.net |
2 redirects
www.googletagmanager.com
|
| 3 | js.zi-scripts.com |
www.paycom.com
js.zi-scripts.com |
| 3 | js.adsrvr.org |
www.googletagmanager.com
match.adsrvr.org |
| 2 | 15036603.fls.doubleclick.net |
1 redirects
www.googletagmanager.com
|
| 2 | scout.salesloft.com |
scout-cdn.salesloft.com
|
| 2 | cm.g.doubleclick.net | 2 redirects |
| 2 | dpm.demdex.net | 2 redirects |
| 2 | connect.facebook.net |
www.paycom.com
connect.facebook.net |
| 2 | munchkin.marketo.net |
www.paycom.com
munchkin.marketo.net |
| 2 | snap.licdn.com |
www.googletagmanager.com
snap.licdn.com |
| 2 | cdn.vidyard.com |
www.paycom.com
|
| 1 | adservice.google.com |
15036603.fls.doubleclick.net
|
| 1 | analytics-ipv6.tiktokw.us |
analytics.tiktok.com
|
| 1 | www.facebook.com | |
| 1 | 502-gzq-487.mktoresp.com |
munchkin.marketo.net
|
| 1 | www.linkedin.com | 1 redirects |
| 1 | ws-assets.zoominfo.com |
js.zi-scripts.com
|
| 1 | verifi.podscribe.com | |
| 1 | pixel.rubiconproject.com | 1 redirects |
| 1 | stats.g.doubleclick.net |
www.googletagmanager.com
|
| 1 | analytics.google.com |
www.googletagmanager.com
|
| 1 | tracking-api.g2.com |
tracking.g2crowd.com
|
| 1 | ipv4.podscribe.com |
d34r8q7sht0t9k.cloudfront.net
|
| 1 | analytics.twitter.com | |
| 1 | t.co | |
| 1 | googleads.g.doubleclick.net |
www.googletagmanager.com
|
| 1 | scout-cdn.salesloft.com |
www.paycom.com
|
| 1 | d34r8q7sht0t9k.cloudfront.net |
www.paycom.com
|
| 1 | b.videoamp.com | |
| 1 | tracking.g2crowd.com |
www.paycom.com
|
| 1 | static.ads-twitter.com |
www.googletagmanager.com
|
| 1 | cdn.jsdelivr.net |
www.paycom.com
|
| 1 | geolocation.onetrust.com |
cdn.cookielaw.org
|
| 1 | www.paycomonline.com | 1 redirects |
| 1 | test-app.rpspayroll.org | 1 redirects |
| 0 | s.ml-attr.com Failed | |
| 156 | 49 |
This site contains links to these domains. Also see Links.
| Subject Issuer | Validity | Valid | |
|---|---|---|---|
| *.paycom.com DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2026-04-30 - 2026-11-14 |
7mo | crt.sh |
| cookielaw.org WE1 |
2026-09-19 - 2026-12-19 |
3mo | crt.sh |
| cdn.paycom.com DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2026-01-16 - 2027-02-16 |
1yr | crt.sh |
| *.vidyard.com GlobalSign Atlas R3 DV TLS CA 2025 Q4 |
2025-12-09 - 2027-01-10 |
1yr | crt.sh |
| *.google-analytics.com WR2 |
2026-09-10 - 2026-12-03 |
3mo | crt.sh |
| geolocation.onetrust.com WE1 |
2026-09-19 - 2026-12-18 |
3mo | crt.sh |
| *.jsdelivr.net Sectigo Public Server Authentication CA DV R36 |
2026-04-22 - 2026-11-06 |
7mo | crt.sh |
| ads-twitter.com YR2 |
2026-09-14 - 2026-12-13 |
3mo | crt.sh |
| www.bing.com Microsoft TLS G2 RSA CA OCSP 04 |
2026-09-01 - 2027-02-28 |
6mo | crt.sh |
| *.licdn.com DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2026-09-08 - 2027-03-25 |
7mo | crt.sh |
| *.marketo.net DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2026-08-24 - 2027-03-10 |
7mo | crt.sh |
| *.adsrvr.org GlobalSign GCC R3 DV TLS CA 2020 |
2026-03-04 - 2027-04-02 |
1yr | crt.sh |
| g2crowd.com WE1 |
2026-09-28 - 2026-12-27 |
3mo | crt.sh |
| *.tiktok.com RapidSSL TLS ECC CA G1 |
2026-05-19 - 2026-12-03 |
7mo | crt.sh |
| *.facebook.com DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2026-07-16 - 2026-10-14 |
3mo | crt.sh |
| zi-scripts.com WE1 |
2026-08-31 - 2026-11-29 |
3mo | crt.sh |
| *.google.com WR2 |
2026-09-10 - 2026-12-03 |
3mo | crt.sh |
| *.doubleclick.net WR2 |
2026-09-10 - 2026-12-03 |
3mo | crt.sh |
| *.videoamp.com Amazon RSA 2048 M01 |
2026-10-06 - 2027-04-21 |
7mo | crt.sh |
| *.cloudfront.net Amazon RSA 2048 M04 |
2026-08-25 - 2027-03-10 |
7mo | crt.sh |
| salesloft.com Sectigo Public Server Authentication CA DV R36 |
2026-09-24 - 2027-04-10 |
7mo | crt.sh |
| *.g.doubleclick.net WR2 |
2026-09-10 - 2026-12-03 |
3mo | crt.sh |
| t.co YE2 |
2026-09-06 - 2026-12-05 |
3mo | crt.sh |
| *.twitter.com YR1 |
2026-09-28 - 2026-12-27 |
3mo | crt.sh |
| ipv4.podscribe.com Amazon RSA 2048 M01 |
2026-01-29 - 2027-02-27 |
1yr | crt.sh |
| tracking-api.g2.com WE1 |
2026-09-01 - 2026-11-30 |
3mo | crt.sh |
| *.podscribe.com Amazon RSA 2048 M04 |
2026-08-28 - 2027-03-13 |
7mo | crt.sh |
| zoominfo.com YE1 |
2026-09-20 - 2026-12-19 |
3mo | crt.sh |
| *.mktoresp.com DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2026-07-27 - 2027-02-10 |
7mo | crt.sh |
| *.tiktokw.us RapidSSL TLS ECC CA G1 |
2026-06-09 - 2026-12-24 |
7mo | crt.sh |
| www.linkedin.com DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2026-08-22 - 2027-02-22 |
6mo | crt.sh |
This page contains 10 frames:
Primary Page:
https://www.paycom.com/
Frame ID: 9DD76EB0B046DB68E6038F80B243C549
Requests: 139 HTTP requests in this frame
Frame:
https://match.adsrvr.org/track/cei?advertiser_id=mu2tm0y&cookie_sync=1&upv=3.0.0&upid=00fsog4&ref=https%3a%2f%2fwww.paycom.com&redirect=1
Frame ID: 569867CAFA9912DB4F2FF2544B31D5F6
Requests: 2 HTTP requests in this frame
Frame:
https://match.adsrvr.org/track/cei?advertiser_id=cgwcuru&cookie_sync=1&upv=3.0.0&upid=lz72rpt&ref=https%3a%2f%2fwww.paycom.com&redirect=1
Frame ID: 7980E2135DB086CA9988FD1E46DAF8DB
Requests: 2 HTTP requests in this frame
Frame:
https://match.adsrvr.org/track/cmf/generic?ttd_pid=aam
Frame ID: BAB670E00493A03C8054B346AE4BE7ED
Requests: 1 HTTP requests in this frame
Frame:
https://match.adsrvr.org/track/cmf/appnexus?ttd=1&anid=8479623455935925714&ttd_tdid=4333c6f4-5603-4421-9023-4dce73762881
Frame ID: C8EC7B0A2430C0CEAA544F847C4429B3
Requests: 1 HTTP requests in this frame
Frame:
https://match.adsrvr.org/track/cmf/google?g_uuid=&gdpr=0&gdpr_consent=&ttd_tdid=4333c6f4-5603-4421-9023-4dce73762881&google_gid=CAESECtGQUnU9nOh9-uTnCZWJo0&google_cver=1
Frame ID: 467AE1E76E0AE8A57524EBD3C6B1978F
Requests: 1 HTTP requests in this frame
Frame:
https://match.adsrvr.org/track/cmf/appnexus?ttd=1&anid=3896039076974146054&ttd_tdid=4333c6f4-5603-4421-9023-4dce73762881
Frame ID: 15132BA8C513AE167E1C6213430BDAE8
Requests: 1 HTTP requests in this frame
Frame:
https://match.adsrvr.org/track/cmf/google?g_uuid=&gdpr=0&gdpr_consent=&ttd_tdid=4333c6f4-5603-4421-9023-4dce73762881&google_gid=CAESEIe0JaaGzead_fzip6IZmrs&google_cver=1
Frame ID: 8A497CE1395B8C96CE06A9A41E05000F
Requests: 1 HTTP requests in this frame
Frame:
https://match.adsrvr.org/track/cmf/rubicon?gdpr=0
Frame ID: D438A15FA6D2D7E67118668E3F3E782E
Requests: 1 HTTP requests in this frame
Frame:
https://15036603.fls.doubleclick.net/activityi;dc_pre=CLqeloK9p5cDFfUNVwEdKB04vg;src=15036603;type=pageview;cat=allpages;rcb=16;ord=5921804078231;npa=0;auiddc=2096428723.1791361338;u1=https%3A%2F%2Fwww.paycom.com%2F;uaa=x86;uab=64;uafvl=Chromium%3B154.0.8037.97%7CGoogle%2520Chrome%3B154.0.8037.97%7CNot%2520A(Brand%3B99.0.0.0;uamb=0;uam=;uap=Linux;uapv=;uaw=0;pscdl=noapi;frm=0;_tu=KFA;gtm=45fe6a51v9200645346z877609891za20gzb77609891zd77609891xeaxf1;gcd=13l3l3l3l1l1;dma=0;dc_fmt=2;tag_exp=115938466~115938469~118131809~118897920~118897930~120213116~120385422~120469145~120469153~121046263~121046271~121280970;epver=2;dc_random=1791361338_yek8oc486NDkO1nexT0b9tFyhQdAMS-6kg;_dc_test=1;~oref=https%3A%2F%2Fwww.paycom.com%2F
Frame ID: 7B530D50DB6DD8E2C206F09B1BEB856A
Requests: 2 HTTP requests in this frame
Screenshot
Go Pro
Only in urlscan Pro
Use the Visual Search feature to find pages with visually similar screenshots.
Click for more information
Free trials of urlscan Pro are available.
Page Title
The #1 HR and Payroll Software | PaycomPage URL History
Go Pro
Only in urlscan Pro
Search our real-time database of newly observed domains and
hostnames. Pivot on different attributes, and setup keyword alerts for
newly observed domains.
Click for more information
Free trials of urlscan Pro are available.
Show full URLs
-
http://test-app.rpspayroll.org/
HTTP 307
https://test-app.rpspayroll.org/ HTTP 301
https://www.paycomonline.com/ HTTP 301
https://www.paycom.com/ Page URL
Detected technologies
 Bootstrap
(UI frameworks)
Expand
Detected patterns
- <link[^>]* href=[^>]*?bootstrap(?:[^>]*?([0-9a-fA-F]{7,40}|[\d]+(?:.[\d]+(?:.[\d]+)?)?)|)[^>-]*?(?:\.min)?\.css
- (?:/|-)bootstrap(?:[^/]*?([0-9a-fA-F]{7,40}|[\d]+(?:\.[\d]+(?:\.[\d]+)?)?)|)[^/]*?(?:\.min)?\.js
 Adobe Audience Manager
(Segmentation)
Expand
Detected patterns
 Cloudflare Bot Management
(Security)
Expand
Detected patterns
 DoubleClick Floodlight
(Advertising)
Expand
Detected patterns
- \.doubleclick\.net
 Facebook Pixel
(Analytics)
Expand
Detected patterns
- connect\.facebook\.\w+/.+/fbevents\.js
- connect\.facebook.\w+/signals/config/\d+\?v=([\d\.]+)
 Font Awesome
(Font scripts)
Expand
Detected patterns
- (?:F|f)o(?:n|r)t-?(?:A|a)wesome(?:.*?([0-9a-fA-F]{7,40}|[\d]+(?:.[\d]+(?:.[\d]+)?)?)|)
 Google Analytics
(Analytics)
Expand
Detected patterns
- googletagmanager\.com/gtag/js
 Google Tag Manager
(Tag managers)
Expand
Detected patterns
- <!-- (?:End )?Google Tag Manager -->
- googletagmanager\.com/gtm\.js
- \.googletagmanager\.com/
 jQuery
(JavaScript libraries)
Expand
Detected patterns
- jquery
- /jquery(?:-(\d+\.\d+\.\d+))[/.-]
 jsDelivr
(CDN)
Expand
Detected patterns
- cdn\.jsdelivr\.net
 Linkedin Insight Tag
(Analytics)
Expand
Detected patterns
- snap\.licdn\.com/li\.lms-analytics/insight\.min\.js
 Marketo
(Marketing automation)
Expand
Detected patterns
- munchkin\.marketo\.\w+/(?:([\d.]+)/)?munchkin\.js
 Microsoft Advertising
(Advertising)
Expand
Detected patterns
- bat\.bing\.com/bat\.js
- \w+
 OneTrust
(Cookie compliance)
Expand
Detected patterns
- cdn\.cookielaw\.org
- otSDKStub\.js
 Podscribe
(Advertising)
Expand
Detected patterns
- podscribe\.(?:ai|com)/
 Slick
(JavaScript libraries)
Expand
Detected patterns
- (?:/([\d.]+))?/slick(?:\.min)?\.js
 theTradeDesk
(Advertising)
Expand
Detected patterns
- \.adsrvr\.org/
 Twitter Ads
(Advertising)
Expand
Detected patterns
- static\.ads-twitter\.com/uwt\.js
Twitter Analytics
(Analytics)
Expand
Detected patterns
- analytics\.twitter\.com
 Zoominfo
(Analytics)
Expand
Detected patterns
- ws\.zoominfo\.com
 PyScript
(Miscellaneous)
Expand
Detected patterns
Page Statistics
18 Outgoing links
Go Pro
Only in urlscan Pro
Effortlessly use any on-page link as a pivot to discover other pages pointing to the exact same destination. Seamlessly trace both specific URLs and broader domains to uncover hidden connection networks and map out backlink relationships with ease.
Click for more information
Free trials of urlscan Pro are available.
These are links going to different origins than the main page.
Title: Client
Search URL Search Domain Scan URL
Title: Employee
Search URL Search Domain Scan URL
Title: Accountant
Search URL Search Domain Scan URL
Title: COBRA Account
Search URL Search Domain Scan URL
Title: investors
Search URL Search Domain Scan URL
Title: Global HCM™
Search URL Search Domain Scan URL
Title: Apply Now
Search URL Search Domain Scan URL
Title: Investors
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Title: More information
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Page URL History
This captures the URL locations of the websites, including HTTP redirects and client-side redirects via JavaScript or Meta fields.
-
http://test-app.rpspayroll.org/
HTTP 307
https://test-app.rpspayroll.org/ HTTP 301
https://www.paycomonline.com/ HTTP 301
https://www.paycom.com/ Page URL
Redirected requests
There were HTTP redirect chains for the following requests:
Request Chain 22- https://play.vidyard.com/JY3gmVfDKPw29ZnMp7ScQq.jpg HTTP 302
- https://cdn.vidyard.com/thumbnails/43622151/zECjusEltn6wDiWJsHfuZA.jpg
- https://play.vidyard.com/2ijFV6mwrVY8tnNYCK1gvL.jpg HTTP 302
- https://cdn.vidyard.com/thumbnails/49690854/ouRgYOXrLuGo-T_M1tC0hA.png
- https://insight.adsrvr.org/track/cei?advertiser_id=mu2tm0y&cookie_sync=1&upv=3.0.0&upid=00fsog4&ref=https%3A%2F%2Fwww.paycom.com%2F HTTP 302
- https://match.adsrvr.org/track/cei?advertiser_id=mu2tm0y&cookie_sync=1&upv=3.0.0&upid=00fsog4&ref=https%3a%2f%2fwww.paycom.com&redirect=1
- https://insight.adsrvr.org/track/cei?advertiser_id=cgwcuru&cookie_sync=1&upv=3.0.0&upid=lz72rpt&ref=https%3A%2F%2Fwww.paycom.com%2F HTTP 302
- https://match.adsrvr.org/track/cei?advertiser_id=cgwcuru&cookie_sync=1&upv=3.0.0&upid=lz72rpt&ref=https%3a%2f%2fwww.paycom.com&redirect=1
- https://dpm.demdex.net/ibs:dpid=903&dpuuid=4333c6f4-5603-4421-9023-4dce73762881&gdpr=0&gdpr_consent=&redir=https%3A%2F%2Fmatch.adsrvr.org%2Ftrack%2Fcmf%2Fgeneric%3Fttd_pid%3Daam HTTP 302
- https://dpm.demdex.net/demconf.jpg?et:ibs%7cdata:dpid=903&dpuuid=4333c6f4-5603-4421-9023-4dce73762881&gdpr=0&gdpr_consent=&redir=https%3A%2F%2Fmatch.adsrvr.org%2Ftrack%2Fcmf%2Fgeneric%3Fttd_pid%3Daam HTTP 302
- https://match.adsrvr.org/track/cmf/generic?ttd_pid=aam
- https://ib.adnxs.com/getuid?https%3a%2f%2fmatch.adsrvr.org%2ftrack%2fcmf%2fappnexus%3fttd%3d1%26anid%3d%24UID&ttd_tdid=4333c6f4-5603-4421-9023-4dce73762881 HTTP 307
- https://ib.adnxs.com/bounce?%2Fgetuid%3Fhttps%253a%252f%252fmatch.adsrvr.org%252ftrack%252fcmf%252fappnexus%253fttd%253d1%2526anid%253d%2524UID%26ttd_tdid%3D4333c6f4-5603-4421-9023-4dce73762881 HTTP 302
- https://match.adsrvr.org/track/cmf/appnexus?ttd=1&anid=8479623455935925714&ttd_tdid=4333c6f4-5603-4421-9023-4dce73762881
- https://cm.g.doubleclick.net/pixel?google_nid=TheTradeDesk&google_cm&google_sc&google_hm=NDMzM2M2ZjQtNTYwMy00NDIxLTkwMjMtNGRjZTczNzYyODgx&gdpr=0&gdpr_consent=&ttd_tdid=4333c6f4-5603-4421-9023-4dce73762881 HTTP 302
- https://match.adsrvr.org/track/cmf/google?g_uuid=&gdpr=0&gdpr_consent=&ttd_tdid=4333c6f4-5603-4421-9023-4dce73762881&google_gid=CAESECtGQUnU9nOh9-uTnCZWJo0&google_cver=1
- https://ib.adnxs.com/getuid?https%3a%2f%2fmatch.adsrvr.org%2ftrack%2fcmf%2fappnexus%3fttd%3d1%26anid%3d%24UID&ttd_tdid=4333c6f4-5603-4421-9023-4dce73762881 HTTP 307
- https://ib.adnxs.com/bounce?%2Fgetuid%3Fhttps%253a%252f%252fmatch.adsrvr.org%252ftrack%252fcmf%252fappnexus%253fttd%253d1%2526anid%253d%2524UID%26ttd_tdid%3D4333c6f4-5603-4421-9023-4dce73762881 HTTP 302
- https://match.adsrvr.org/track/cmf/appnexus?ttd=1&anid=3896039076974146054&ttd_tdid=4333c6f4-5603-4421-9023-4dce73762881
- https://cm.g.doubleclick.net/pixel?google_nid=TheTradeDesk&google_cm&google_sc&google_hm=NDMzM2M2ZjQtNTYwMy00NDIxLTkwMjMtNGRjZTczNzYyODgx&gdpr=0&gdpr_consent=&ttd_tdid=4333c6f4-5603-4421-9023-4dce73762881 HTTP 302
- https://match.adsrvr.org/track/cmf/google?g_uuid=&gdpr=0&gdpr_consent=&ttd_tdid=4333c6f4-5603-4421-9023-4dce73762881&google_gid=CAESEIe0JaaGzead_fzip6IZmrs&google_cver=1
- https://pixel.rubiconproject.com/tap.php?v=8981&nid=2307&put=4333c6f4-5603-4421-9023-4dce73762881&gdpr=0&gdpr_consent=&expires=30&next=https%3A%2F%2Fmatch.adsrvr.org%2Ftrack%2Fcmf%2Frubicon HTTP 302
- https://match.adsrvr.org/track/cmf/rubicon?gdpr=0
- https://px.ads.linkedin.com/collect?v=2&fmt=js&pid=227594&time=1791361338573&li_adsId=22577e76-9516-42e2-84d5-59847536853b&pageLoadId=0fe261f2-e674-4fc3-a46a-70bba45c7835&url=https%3A%2F%2Fwww.paycom.com%2F HTTP 302
- https://px.ads.linkedin.com/collect?v=2&fmt=js&pid=227594&time=1791361338573&li_adsId=22577e76-9516-42e2-84d5-59847536853b&pageLoadId=0fe261f2-e674-4fc3-a46a-70bba45c7835&url=https%3A%2F%2Fwww.paycom.com%2F&cookiesTest=true HTTP 302
- https://www.linkedin.com/px/li_sync?redirect=https%3A%2F%2Fpx.ads.linkedin.com%2Fcollect%3Fv%3D2%26fmt%3Djs%26pid%3D227594%26time%3D1791361338573%26li_adsId%3D22577e76-9516-42e2-84d5-59847536853b%26pageLoadId%3D0fe261f2-e674-4fc3-a46a-70bba45c7835%26url%3Dhttps%253A%252F%252Fwww.paycom.com%252F%26cookiesTest%3Dtrue%26liSync%3Dtrue HTTP 302
- https://px.ads.linkedin.com/collect?v=2&fmt=js&pid=227594&time=1791361338573&li_adsId=22577e76-9516-42e2-84d5-59847536853b&pageLoadId=0fe261f2-e674-4fc3-a46a-70bba45c7835&url=https%3A%2F%2Fwww.paycom.com%2F&cookiesTest=true&liSync=true
- https://ad.doubleclick.net/activity;src=15036603;type=pageview;cat=allpages;rcb=16;ord=5921804078231;npa=0;auiddc=2096428723.1791361338;u1=https%3A%2F%2Fwww.paycom.com%2F;uaa=x86;uab=64;uafvl=Chromium%3B154.0.8037.97%7CGoogle%2520Chrome%3B154.0.8037.97%7CNot%2520A(Brand%3B99.0.0.0;uamb=0;uam=;uap=Linux;uapv=;uaw=0;pscdl=noapi;frm=0;_tu=KFA;gtm=45fe6a51v9200645346z877609891za20gzb77609891zd77609891xeaxf1;gcd=13l3l3l3l1l1;dma=0;dc_fmt=3;tag_exp=115938466~115938469~118131809~118897920~118897930~120213116~120385422~120469145~120469153~121046263~121046271~121280970;epver=2;dc_random=1791361338_yek8oc486NDkO1nexT0b9tFyhQdAMS-6kg;~oref=https%3A%2F%2Fwww.paycom.com%2F HTTP 302
- https://ad.doubleclick.net/activity;dc_pre=CP72k4K9p5cDFUxpKQYdwFQAiw;src=15036603;type=pageview;cat=allpages;rcb=16;ord=5921804078231;npa=0;auiddc=2096428723.1791361338;u1=https%3A%2F%2Fwww.paycom.com%2F;uaa=x86;uab=64;uafvl=Chromium%3B154.0.8037.97%7CGoogle%2520Chrome%3B154.0.8037.97%7CNot%2520A(Brand%3B99.0.0.0;uamb=0;uam=;uap=Linux;uapv=;uaw=0;pscdl=noapi;frm=0;_tu=KFA;gtm=45fe6a51v9200645346z877609891za20gzb77609891zd77609891xeaxf1;gcd=13l3l3l3l1l1;dma=0;dc_fmt=3;tag_exp=115938466~115938469~118131809~118897920~118897930~120213116~120385422~120469145~120469153~121046263~121046271~121280970;epver=2;dc_random=1791361338_yek8oc486NDkO1nexT0b9tFyhQdAMS-6kg;~oref=https%3A%2F%2Fwww.paycom.com%2F HTTP 302
- https://www.google.com/gmp/conversion/_dc_unique_id=17134358201351622868;_dc_ptd=ChEI8NuX1gYQo7OzxLaP2M6sARIfAOYp2PbXDr12aX1kzwc2IwQEGutcs0aOVzfzUHClZA;_dc_time=1791361338;cid=CAQS4gEAQM4h3MPtTuxIUdDzaorVA7NrsVuM73qhk54nrQW_OMdAY5LmnVRNaoKEncjRnt3nt9qaVpkUd9ifuzm7U2RW4s0SFAi7ZbWABuME-AkDhpXA13zCbTVmNUhH3gGLcxYS0yOo7Vr9bH1oTKzp8v6j6S22aMUan0m-eMkkUJC5XV5DrHe8w5TEo7GomzlG6KyPuVqL5hDocnoY8wXUe4kUV0oiNeDcRKPrX4pcw8iCvLmBIiihWNukMJWH-yoZOAb1ZnIU0x26a0xcVI4eFL6lNus475-RB2nwO8OU-2_yUB2H;eps=AHas8cCJbmuMKABLQJpgsWKZkqkr_Xp0KVfbkyGFdnUXljPtswjbuErjxVenH4TdpetZkbZYtIj282duDKyisiY9Om5JTajqqYNr0XmdmAyjfcF4nA;dc_pre=CP72k4K9p5cDFUxpKQYdwFQAiw;src=15036603;type=pageview;cat=allpages;rcb=16;ord=5921804078231;npa=0;auiddc=2096428723.1791361338;u1=https%3A%2F%2Fwww.paycom.com%2F;uaa=x86;uab=64;uafvl=Chromium%3B154.0.8037.97%7CGoogle%2520Chrome%3B154.0.8037.97%7CNot%2520A(Brand%3B99.0.0.0;uamb=0;uam=;uap=Linux;uapv=;uaw=0;pscdl=noapi;frm=0;_tu=KFA;gtm=45fe6a51v9200645346z877609891za20gzb77609891zd77609891xeaxf1;gcd=13l3l3l3l1l1;dma=0;dc_fmt=3;tag_exp=115938466~115938469~118131809~118897920~118897930~120213116~120385422~120469145~120469153~121046263~121046271~121280970;epver=2;dc_random=1791361338_yek8oc486NDkO1nexT0b9tFyhQdAMS-6kg;~oref=https%3A%2F%2Fwww.paycom.com%2F
- https://15036603.fls.doubleclick.net/activityi;src=15036603;type=pageview;cat=allpages;rcb=16;ord=5921804078231;npa=0;auiddc=2096428723.1791361338;u1=https%3A%2F%2Fwww.paycom.com%2F;uaa=x86;uab=64;uafvl=Chromium%3B154.0.8037.97%7CGoogle%2520Chrome%3B154.0.8037.97%7CNot%2520A(Brand%3B99.0.0.0;uamb=0;uam=;uap=Linux;uapv=;uaw=0;pscdl=noapi;frm=0;_tu=KFA;gtm=45fe6a51v9200645346z877609891za20gzb77609891zd77609891xeaxf1;gcd=13l3l3l3l1l1;dma=0;dc_fmt=2;tag_exp=115938466~115938469~118131809~118897920~118897930~120213116~120385422~120469145~120469153~121046263~121046271~121280970;epver=2;dc_random=1791361338_yek8oc486NDkO1nexT0b9tFyhQdAMS-6kg;_dc_test=1;~oref=https%3A%2F%2Fwww.paycom.com%2F HTTP 302
- https://15036603.fls.doubleclick.net/activityi;dc_pre=CLqeloK9p5cDFfUNVwEdKB04vg;src=15036603;type=pageview;cat=allpages;rcb=16;ord=5921804078231;npa=0;auiddc=2096428723.1791361338;u1=https%3A%2F%2Fwww.paycom.com%2F;uaa=x86;uab=64;uafvl=Chromium%3B154.0.8037.97%7CGoogle%2520Chrome%3B154.0.8037.97%7CNot%2520A(Brand%3B99.0.0.0;uamb=0;uam=;uap=Linux;uapv=;uaw=0;pscdl=noapi;frm=0;_tu=KFA;gtm=45fe6a51v9200645346z877609891za20gzb77609891zd77609891xeaxf1;gcd=13l3l3l3l1l1;dma=0;dc_fmt=2;tag_exp=115938466~115938469~118131809~118897920~118897930~120213116~120385422~120469145~120469153~121046263~121046271~121280970;epver=2;dc_random=1791361338_yek8oc486NDkO1nexT0b9tFyhQdAMS-6kg;_dc_test=1;~oref=https%3A%2F%2Fwww.paycom.com%2F
156 HTTP transactions
Go Pro
Only in urlscan Pro
Inspect WebSocket connections, examine POST data effortlessly, and track overlap counts in real time. Features live search and filtering across all HTTP output, complete with full response metadata for deep analysis.
Click for more information
Free trials of urlscan Pro are available.
0 data transactions
| Method Protocol |
Status | Resource Path |
Size x-fer |
Time Latency |
Type MIME-Type |
IP Location |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
|
GET H2 |
200 |
Primary Request
/
Show response
www.paycom.com/ Redirect Chain
|
254 KB 59 KB |
245ms
223ms |
Document
text/html |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
jquery-3.7.0.min.js
Show response
www.paycom.com/js/jquery/ |
85 KB 35 KB |
118ms
114ms |
Script
application/javascript |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
http-block-tests.js
Show response
www.paycom.com/js/ |
2 KB 749 B |
271ms
267ms |
Script
application/javascript |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
data-layer.js
Show response
www.paycom.com/js/ |
26 KB 5 KB |
117ms
113ms |
Script
application/javascript |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
otSDKStub.js
Show response
cdn.cookielaw.org/scripttemplates/ |
59 KB 14 KB |
54ms
20ms |
Script
application/javascript |
104.18.87.42 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
bebasneuepro-bold-webfont.woff2
www.paycom.com/fonts/Bebas-Neue-Pro-Regular/ |
22 KB 22 KB |
186ms
183ms |
Font
font/woff2 |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
gb-global-style.build.css
www.paycom.com/css/gb/ |
1 MB 205 KB |
116ms
114ms |
Stylesheet
text/css |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
animate.min.css
www.paycom.com/css/ |
70 KB 7 KB |
267ms
265ms |
Stylesheet
text/css |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
autocomplete-theme-classic.css
www.paycom.com/css/ |
34 KB 7 KB |
230ms
229ms |
Stylesheet
text/css |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
styles.css
www.paycom.com/css/site/homepage/ |
23 KB 5 KB |
267ms
265ms |
Stylesheet
text/css |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
slick.css
www.paycom.com/js/slick-1.8.1/slick/ |
2 KB 658 B |
266ms
265ms |
Stylesheet
text/css |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Hero-Background.png
www.paycom.com/images/home/ |
477 KB 479 KB |
61ms
56ms |
Image
image/png |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
PHONE-Floating2-ARC-ESS-Home.webp
cdn.paycom.com/mkon/www/media/homepage-content/ |
270 KB 270 KB |
450ms
128ms |
Image
image/avif |
23.49.248.11 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
accolade-trustradius-buyers-choice-2026.png
www.paycom.com/images/home/ |
19 KB 19 KB |
100ms
99ms |
Image
image/png |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
accolade-USA-Today-2026.png
www.paycom.com/images/home/ |
15 KB 15 KB |
185ms
185ms |
Image
image/png |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
accolades-G2-Leader-Spring-2026.png
www.paycom.com/images/home/ |
13 KB 13 KB |
71ms
70ms |
Image
image/png |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Newsweek-US-Online-Platforms-2026.png
www.paycom.com/images/home/ |
63 KB 64 KB |
62ms
62ms |
Image
image/png |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
iwant-tm-White.svg
www.paycom.com/images/home/ |
2 KB 1 KB |
159ms
154ms |
Image
image/svg+xml |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
iwant-tm.svg
www.paycom.com/images/home/ |
2 KB 1 KB |
69ms
65ms |
Image
image/svg+xml |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
iwant-sparkle-Track-Green.svg
www.paycom.com/images/home/ |
863 B 546 B |
68ms
64ms |
Image
image/svg+xml |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
professional-client.webp
cdn.paycom.com/mkon/www/media/homepage-content/ |
57 KB 58 KB |
253ms
249ms |
Image
image/webp |
23.49.248.11 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
support-employee.webp
cdn.paycom.com/mkon/www/media/homepage-content/ |
40 KB 41 KB |
262ms
258ms |
Image
image/webp |
23.49.248.11 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
v4.js
Show response
play.vidyard.com/embed/ |
71 KB 23 KB |
26ms
3ms |
Script
application/javascript |
151.101.65.181 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
zECjusEltn6wDiWJsHfuZA.jpg
cdn.vidyard.com/thumbnails/43622151/ Redirect Chain
|
35 KB 36 KB |
46ms
6ms |
Image
image/jpeg |
13.33.67.105 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
slick.min.js
Show response
www.paycom.com/js/slick-1.8.1/slick/ |
42 KB 13 KB |
60ms
57ms |
Script
application/javascript |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
main.min.js
Show response
www.paycom.com/js/site/homepage/ |
8 KB 3 KB |
80ms
77ms |
Script
application/javascript |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
logo-app-store.svg
www.paycom.com/images/mobile-app/ |
8 KB 3 KB |
80ms
78ms |
Image
image/svg+xml |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
logo-play-store.svg
www.paycom.com/images/mobile-app/ |
4 KB 2 KB |
67ms
65ms |
Image
image/svg+xml |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
loading.gif
www.paycom.com/images/ |
723 B 783 B |
59ms
56ms |
Image
image/gif |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
gb-main.min.js
Show response
www.paycom.com/js/gb/ |
25 KB 8 KB |
59ms
57ms |
Script
application/javascript |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
bootstrap.min.js
Show response
www.paycom.com/js/bootstrap-4.3.1/ |
57 KB 19 KB |
60ms
58ms |
Script
application/javascript |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
algoliasearch.umd.js
Show response
www.paycom.com/js/algoliasearch/5.52.1/ |
107 KB 19 KB |
79ms
79ms |
Script
application/javascript |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
autocomplete-js.js
Show response
www.paycom.com/js/autocomplete-1.18.1/ |
92 KB 25 KB |
71ms
65ms |
Script
application/javascript |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
autocomplete-plugin-query-suggestions.js
Show response
www.paycom.com/js/autocomplete-1.18.1/ |
12 KB 4 KB |
82ms
77ms |
Script
application/javascript |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
autocomplete.min.js
Show response
www.paycom.com/js/site/modules/AlgoliaSearch/ |
3 KB 1 KB |
82ms
77ms |
Script
application/javascript |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
CookieBanner.min.js
Show response
www.paycom.com/js/site/ |
2 KB 946 B |
82ms
77ms |
Script
application/javascript |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
geopixel.png
www.paycom.com/images/ |
118 B 165 B |
79ms
77ms |
Image
image/png |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
4dd85eaf-443e-4877-b624-dc86d431611c.json
Show response
cdn.cookielaw.org/consent/4dd85eaf-443e-4877-b624-dc86d431611c/ |
5 KB 2 KB |
46ms
25ms |
XHR
application/json |
104.18.87.42 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
gtm.js
Show response
www.googletagmanager.com/ |
617 KB 185 KB |
55ms
37ms |
Script
application/javascript |
142.250.191.8 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
location
Show response
geolocation.onetrust.com/cookieconsentpub/v1/geo/ |
71 B 285 B |
407ms
97ms |
XHR
application/json |
104.18.32.137 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
dedicated-service-top.png
www.paycom.com/images/home/dedicated-service/ |
9 KB 9 KB |
62ms
61ms |
Image
image/png |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
dedicated-service-bottom.png
www.paycom.com/images/home/dedicated-service/ |
18 KB 18 KB |
84ms
83ms |
Image
image/png |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Ratings-star.svg
www.paycom.com/images/home/ |
415 B 336 B |
93ms
92ms |
Image
image/svg+xml |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Patriots-case-study.webp
cdn.paycom.com/mkon/www/media/homepage-content/ |
65 KB 65 KB |
193ms
192ms |
Image
image/webp |
23.49.248.11 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
OpenSans-Regular-webfont.woff2
www.paycom.com/fonts/opensans_regular/ |
16 KB 16 KB |
103ms
97ms |
Font
font/woff2 |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
OpenSans-Bold-webfont.woff2
www.paycom.com/fonts/opensans_bold/ |
16 KB 16 KB |
73ms
67ms |
Font
font/woff2 |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
fa-solid-900.woff2
www.paycom.com/fonts/fontAwesome/ |
147 KB 147 KB |
90ms
85ms |
Font
font/woff2 |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
OpenSans-BoldItalic-webfont.woff
www.paycom.com/fonts/opensans_bolditalic/ |
21 KB 21 KB |
62ms
57ms |
Font
font/woff |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
bebasneuepro-regular-webfont.woff2
www.paycom.com/fonts/Bebas-Neue-Pro-Regular/ |
22 KB 22 KB |
72ms
67ms |
Font
font/woff2 |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
OpenSans-Italic-webfont.woff2
www.paycom.com/fonts/opensans_italic/ |
17 KB 17 KB |
64ms
60ms |
Font
font/woff2 |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
fa-brands-400.woff2
www.paycom.com/fonts/fontAwesome/ |
107 KB 108 KB |
89ms
85ms |
Font
font/woff2 |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
IWant-Poster-Img.png
www.paycom.com/images/home/posters/ |
48 KB 48 KB |
78ms
70ms |
Image
image/png |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
ESS-Overlap-Phones.png
cdn.paycom.com/mkon/www/media/homepage-content/ |
970 KB 971 KB |
128ms
121ms |
Image
image/webp |
23.49.248.11 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Forrester-Logo-White.svg
www.paycom.com/images/home/ |
4 KB 1 KB |
78ms
71ms |
Image
image/svg+xml |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Payroll-Dashboard-Poster-Img.png
www.paycom.com/images/home/posters/ |
62 KB 62 KB |
92ms
85ms |
Image
image/png |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
forrester-logo.svg
www.paycom.com/images/home/ |
8 KB 3 KB |
144ms
137ms |
Image
image/svg+xml |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
algoliaconfig.php
Show response
www.paycom.com/js/autocomplete-1.18.1/ |
183 B 179 B |
157ms
156ms |
Fetch
text/html |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
2ijFV6mwrVY8tnNYCK1gvL
play.vidyard.com/ |
0 2 KB |
11ms
3ms |
Other
text/html |
151.101.65.181 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
ticker.min.js
Show response
www.paycom.com/js/gb/modules/ |
2 KB 915 B |
86ms
85ms |
XHR
application/javascript |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
otBannerSdk.js
Show response
cdn.cookielaw.org/scripttemplates/202510.2.0/ |
513 KB 124 KB |
14ms
14ms |
Script
application/javascript |
104.18.87.42 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
search-insights.min.js
Show response
cdn.jsdelivr.net/npm/search-insights@2.15.0/dist/ |
12 KB 4 KB |
44ms
17ms |
Script
application/javascript |
104.17.207.5 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
en.json
Show response
cdn.cookielaw.org/consent/4dd85eaf-443e-4877-b624-dc86d431611c/0199df41-e4ff-7d6b-95f2-e14efd5058a1/ |
159 KB 28 KB |
23ms
23ms |
Fetch
application/json |
104.18.87.42 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
2ijFV6mwrVY8tnNYCK1gvL.json
Show response
play.vidyard.com/player/ |
17 KB 6 KB |
15ms
14ms |
XHR
application/json |
151.101.65.181 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
style.js
Show response
play.vidyard.com/v4/2ijFV6mwrVY8tnNYCK1gvL/ |
176 B 240 B |
13ms
13ms |
Script
text/javascript |
151.101.65.181 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
integrations.js
Show response
play.vidyard.com/v4/2ijFV6mwrVY8tnNYCK1gvL/ |
201 B 367 B |
13ms
13ms |
Script
text/javascript |
151.101.65.181 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
details.js
Show response
play.vidyard.com/v4/2ijFV6mwrVY8tnNYCK1gvL/ |
152 B 264 B |
12ms
12ms |
Script
text/javascript |
151.101.65.181 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
ouRgYOXrLuGo-T_M1tC0hA.png
cdn.vidyard.com/thumbnails/49690854/ Redirect Chain
|
101 KB 101 KB |
6ms
6ms |
Image
image/png |
13.33.67.105 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
favicon.ico
www.paycom.com/ |
1 KB 910 B |
51ms
50ms |
Other
image/x-icon |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
js
Show response
www.googletagmanager.com/gtag/ |
549 KB 182 KB |
33ms
32ms |
Script
application/javascript |
142.250.191.8 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
uwt.js
Show response
static.ads-twitter.com/ |
61 KB 17 KB |
62ms
15ms |
Script
application/javascript |
146.75.28.157 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
bat.js
Show response
bat.bing.com/ |
54 KB 16 KB |
62ms
17ms |
Script
application/javascript |
150.171.28.10 Microsoft Corpora... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
insight.min.js
Show response
snap.licdn.com/li.lms-analytics/ |
3 KB 2 KB |
54ms
9ms |
Script
application/javascript |
23.200.3.22 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
munchkin.js
Show response
munchkin.marketo.net/ |
1 KB 1 KB |
57ms
18ms |
Script
application/x-javascript |
23.13.173.12 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
/
Show response
www.paycom.com/includes/Facebook/ |
18 B 89 B |
251ms
248ms |
XHR
text/html |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
js
Show response
www.googletagmanager.com/gtag/ |
483 KB 163 KB |
40ms
39ms |
Script
application/javascript |
142.250.191.8 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
up_loader.1.1.0.js
Show response
js.adsrvr.org/ |
45 KB 15 KB |
40ms
7ms |
Script
application/javascript |
13.32.241.20 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
404.js
Show response
tracking.g2crowd.com/attribution_tracking/conversions/ |
4 KB 2 KB |
96ms
64ms |
Script
text/javascript |
104.18.30.176 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
events.js
Show response
analytics.tiktok.com/i18n/pixel/ |
9 KB 3 KB |
97ms
26ms |
Script
application/javascript |
23.40.18.49 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
fbevents.js
Show response
connect.facebook.net/en_US/ |
419 KB 110 KB |
36ms
5ms |
Script
application/x-javascript |
57.144.180.128 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
events.js
Show response
analytics.tiktok.com/i18n/pixel/ |
9 KB 3 KB |
93ms
24ms |
Script
application/javascript |
23.40.18.49 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
zi-tag.js
Show response
js.zi-scripts.com/ |
19 KB 6 KB |
44ms
16ms |
Script
application/javascript |
104.18.37.212 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
otFlat.json
Show response
cdn.cookielaw.org/scripttemplates/202510.2.0/assets/ |
15 KB 3 KB |
19ms
15ms |
Fetch
application/json |
104.18.87.42 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
otPcTab.json
Show response
cdn.cookielaw.org/scripttemplates/202510.2.0/assets/v2/ |
67 KB 14 KB |
31ms
27ms |
Fetch
application/json |
104.18.87.42 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
otCommonStyles.css
Show response
cdn.cookielaw.org/scripttemplates/202510.2.0/assets/ |
26 KB 5 KB |
32ms
29ms |
Fetch
text/css |
104.18.87.42 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
200 |
collect
www.google.com/ccm/ |
0 0 |
45ms
32ms |
Fetch
text/plain |
142.251.153.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
204 |
collect
ad.doubleclick.net/ccm/s/ |
0 0 |
42ms
26ms |
Fetch
text/html |
142.251.45.198 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
impression
b.videoamp.com/d2/b40dac67-266a-4ee4-864d-b3bd2fea7e8c/14112/ |
42 B 312 B |
94ms
59ms |
Image
image/gif |
13.223.123.134 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
getuid
s.ml-attr.com/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
tag.js
Show response
d34r8q7sht0t9k.cloudfront.net/ |
14 KB 6 KB |
35ms
5ms |
Script
text/javascript |
13.226.103.193 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
sl.js
Show response
scout-cdn.salesloft.com/ |
6 KB 3 KB |
69ms
19ms |
Script
text/javascript |
104.19.164.102 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
insight.old.min.js
Show response
snap.licdn.com/li.lms-analytics/ |
61 KB 21 KB |
44ms
42ms |
Script
application/javascript |
23.200.3.22 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
x-icon.png
www.paycom.com/images/icons/ |
364 B 435 B |
61ms
61ms |
Image
image/png |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
ot_guard_logo.svg
Show response
cdn.cookielaw.org/logos/static/ |
497 B 505 B |
15ms
14ms |
Fetch
image/svg+xml |
104.18.87.42 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Paycom_Logo_Green_Black.png
cdn.cookielaw.org/logos/bb7a3bdf-cc37-40db-94e4-0faa9cb15daf/019a978b-9ece-7869-baba-6322b70add46/530af5f9-ea7a-424c-9eb2-a2d08ef74d54/ |
14 KB 14 KB |
16ms
16ms |
Image
image/png |
104.18.87.42 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
powered_by_logo.svg
cdn.cookielaw.org/logos/static/ |
5 KB 3 KB |
27ms
27ms |
Image
image/svg+xml |
104.18.87.42 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
favicon.ico
www.paycom.com/ |
1 KB 0 |
0ms
0ms |
Other
image/x-icon |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
/
Show response
googleads.g.doubleclick.net/pagead/viewthroughconversion/1025213832/ |
6 KB 3 KB |
49ms
33ms |
Script
text/javascript |
142.250.68.194 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
200 |
/
www.google.com/rmkt/collect/1025213832/ |
0 0 |
30ms
30ms |
Fetch
text/html |
142.251.153.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
200 |
collect
www.google.com/ccm/ |
0 0 |
24ms
23ms |
Fetch
text/plain |
142.251.153.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
favicon.ico
www.paycom.com/ |
1 KB 0 |
0ms
0ms |
Other
image/x-icon |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
cei
Show response
match.adsrvr.org/track/ Frame 5698 Redirect Chain
|
1 KB 1 KB |
52ms
45ms |
Document
text/html |
3.33.220.150 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
cei
Show response
match.adsrvr.org/track/ Frame 7980 Redirect Chain
|
1 KB 1 KB |
99ms
93ms |
Document
text/html |
3.33.220.150 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
getSubscriptions
Show response
js.zi-scripts.com/unified/v1/master/ |
566 B 816 B |
87ms
87ms |
Fetch
application/json |
104.18.37.212 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
OPTIONS H3 |
204 |
getSubscriptions
js.zi-scripts.com/unified/v1/master/ Frame |
0 0 |
103ms
85ms |
Preflight
|
104.18.37.212 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
favicon-32x32.png
www.paycom.com/images/favicons/ |
559 B 610 B |
55ms
54ms |
Other
image/png |
107.162.254.104 F5 F5 Networks SARL |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
munchkin.js
Show response
munchkin.marketo.net/165/ |
13 KB 6 KB |
15ms
15ms |
Script
application/x-javascript |
23.13.173.12 Akamai Technologies |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
adsct
t.co/i/ |
43 B 668 B |
88ms
60ms |
Image
image/gif |
162.159.140.229 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
adsct
analytics.twitter.com/i/ |
43 B 687 B |
94ms
58ms |
Image
image/gif |
172.66.0.227 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
23005099.js
Show response
bat.bing.com/p/action/ |
3 KB 1 KB |
19ms
18ms |
Script
application/javascript |
150.171.28.10 Microsoft Corpora... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
/
Show response
ipv4.podscribe.com/ |
24 B 224 B |
89ms
59ms |
Fetch
application/json |
35.170.37.64 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
247293369123592
Show response
connect.facebook.net/signals/config/ |
391 KB 97 KB |
8ms
7ms |
Script
application/x-javascript |
57.144.180.128 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
200 |
assign
tracking-api.g2.com/attribution_tracking/conversions/ |
0 0 |
48ms
35ms |
Ping
text/html |
104.16.188.41 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
main.MWU2MzIzODM0MQ.js
Show response
analytics.tiktok.com/i18n/pixel/static/ |
485 KB 115 KB |
11ms
9ms |
Script
application/javascript |
23.40.18.49 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
destination
Show response
www.googletagmanager.com/gtag/ |
405 KB 141 KB |
32ms
31ms |
Script
application/javascript |
142.250.191.8 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
collect
analytics.google.com/g/ |
0 0 |
100ms
52ms |
Fetch
text/plain |
142.251.45.206 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
collect
stats.g.doubleclick.net/g/ |
0 558 B |
110ms
61ms |
Ping
text/plain |
172.253.62.157 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
universal_pixel.js
Show response
js.adsrvr.org/ Frame 5698 |
482 B 996 B |
54ms
45ms |
Script
application/javascript |
13.32.241.107 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
200 OK |
universal_pixel.js
Show response
js.adsrvr.org/ Frame 7980 |
482 B 443 B |
52ms
4ms |
Script
application/javascript |
13.32.241.107 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
generic
Show response
match.adsrvr.org/track/cmf/ Frame BAB6 Redirect Chain
|
70 B 464 B |
13ms
12ms |
Document
image/gif |
3.33.220.150 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
appnexus
Show response
match.adsrvr.org/track/cmf/ Frame C8EC Redirect Chain
|
70 B 464 B |
11ms
11ms |
Document
image/gif |
3.33.220.150 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
google
Show response
match.adsrvr.org/track/cmf/ Frame 467A Redirect Chain
|
70 B 464 B |
19ms
19ms |
Document
image/gif |
3.33.220.150 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
appnexus
Show response
match.adsrvr.org/track/cmf/ Frame 1513 Redirect Chain
|
70 B 464 B |
16ms
15ms |
Document
image/gif |
3.33.220.150 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
google
Show response
match.adsrvr.org/track/cmf/ Frame 8A49 Redirect Chain
|
70 B 464 B |
11ms
10ms |
Document
image/gif |
3.33.220.150 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
rubicon
Show response
match.adsrvr.org/track/cmf/ Frame D438 Redirect Chain
|
70 B 464 B |
22ms
22ms |
Document
image/gif |
3.33.220.150 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
tag
verifi.podscribe.com/ |
42 B 238 B |
91ms
57ms |
Image
image/png |
3.228.126.156 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
formcomplete.js
Show response
ws-assets.zoominfo.com/ |
49 KB 14 KB |
67ms
34ms |
Script
application/javascript |
104.16.118.43 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
/
Show response
ws.zoominfo.com/pixel/68a5dcdd0d01e04a69eb8f6a/ |
4 KB 2 KB |
97ms
87ms |
Fetch
text/javascript |
104.16.118.43 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
collect
px.ads.linkedin.com/ Redirect Chain
|
0 491 B |
101ms
100ms |
Image
application/javascript |
172.64.146.215 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
r
Show response
scout.salesloft.com/ |
41 B 495 B |
81ms
51ms |
XHR
application/json |
34.21.100.80 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
/
www.google.com/pagead/1p-user-list/1025213832/ |
42 B 64 B |
25ms
24ms |
Image
image/gif |
142.251.153.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H/1.1 |
200 OK |
visitWebPage
502-gzq-487.mktoresp.com/webevents/ |
2 B 318 B |
359ms
73ms |
Ping
text/plain |
192.28.164.179 Adobe Inc. |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
OPTIONS H3 |
200 |
/
ws.zoominfo.com/pixel/68a5dcdd0d01e04a69eb8f6a/ Frame |
0 0 |
79ms
51ms |
Preflight
text/html |
104.16.118.43 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
23005099
Show response
bat.bing.com/p/conversions/t/ |
816 B 1 KB |
20ms
19ms |
Script
application/x-javascript |
150.171.28.10 Microsoft Corpora... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
204 |
0
bat.bing.com/action/ |
0 359 B |
18ms
17ms |
Image
text/plain |
150.171.28.10 Microsoft Corpora... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
/
www.facebook.com/tr/ |
0 20 B |
18ms
4ms |
Image
text/plain |
57.144.180.1 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
i
Show response
scout.salesloft.com/ |
48 B 535 B |
47ms
46ms |
XHR
application/json |
34.21.100.80 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
identify_0504602d.js
Show response
analytics.tiktok.com/i18n/pixel/static/ |
152 KB 40 KB |
11ms
11ms |
Script
application/javascript |
23.40.18.49 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
enrich_ipv6
analytics-ipv6.tiktokw.us/ipv6/ |
0 977 B |
59ms
34ms |
Ping
text/plain |
23.219.161.114 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
pixel
analytics.tiktok.com/api/v2/ |
0 949 B |
63ms
61ms |
Ping
text/plain |
23.40.18.49 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
pixel
analytics.tiktok.com/api/v2/ |
0 951 B |
111ms
108ms |
Ping
text/plain |
23.40.18.49 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
pixel
analytics.tiktok.com/api/v2/ |
0 948 B |
41ms
39ms |
Ping
text/plain |
23.40.18.49 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
pixel
analytics.tiktok.com/api/v2/ |
0 946 B |
62ms
60ms |
Ping
text/plain |
23.40.18.49 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET BLOB |
200 OK |
fa0d306c-591a-4b39-b1e5-1b9ced7d8a8d
Show response
https://www.paycom.com/ |
4 KB 0 |
Script
text/javascript |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
_dc_unique_id=17134358201351622868;_dc_ptd=ChEI8NuX1gYQo7OzxLaP2M6sARIfAOYp2PbXDr12aX1kzwc2IwQEGutcs0aOVzfzUHClZA;_dc_time=1791361338;cid=CAQS4gEAQM4h3MPtTuxIUdDzaorVA7NrsVuM73qhk54nrQW_OMdAY5LmnVR...
Show response
www.google.com/gmp/conversion/ Redirect Chain
|
42 B 63 B |
105ms
105ms |
Fetch
image/gif |
142.251.153.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
activityi;dc_pre=CLqeloK9p5cDFfUNVwEdKB04vg;src=15036603;type=pageview;cat=allpages;rcb=16;ord=5921804078231;npa=0;auiddc=2096428723.1791361338;u1=https%3A%2F%2Fwww.paycom.com%2F;uaa=x86;uab=64;uaf...
Show response
15036603.fls.doubleclick.net/ Frame 7B53 Redirect Chain
|
903 B 627 B |
34ms
33ms |
Document
text/html |
142.250.217.134 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
0.8.70
Show response
bat.bing.com/p/conversions/s/ |
40 KB 15 KB |
19ms
19ms |
Script
application/javascript |
150.171.28.10 Microsoft Corpora... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
OPTIONS H3 |
200 |
forms
ws.zoominfo.com/formcomplete-v2/ Frame |
0 0 |
46ms
46ms |
Preflight
text/html |
104.16.118.43 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
200 |
forms
Show response
ws.zoominfo.com/formcomplete-v2/ |
2 B 383 B |
49ms
48ms |
Fetch
application/json |
104.16.118.43 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
z
Show response
bat.bing.com/p/conversions/c/ |
0 210 B |
25ms
23ms |
XHR
text/plain |
150.171.28.10 Microsoft Corpora... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
dc_pre=CLqeloK9p5cDFfUNVwEdKB04vg;src=15036603;type=pageview;cat=allpages;rcb=16;ord=5921804078231;npa=0;auiddc=*;u1=https%3A%2F%2Fwww.paycom.com%2F;uaa=x86;uab=64;uafvl=Chromium%3B154.0.8037.97%7C...
adservice.google.com/ddm/fls/z/ Frame 7B53 |
42 B 63 B |
43ms
30ms |
Image
image/gif |
142.250.65.66 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
204 |
/
px.ads.linkedin.com/wa/ |
0 0 |
106ms
105ms |
Fetch
|
172.64.146.215 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
act
analytics.tiktok.com/api/v2/pixel/ |
0 951 B |
56ms
52ms |
Ping
text/plain |
23.40.18.49 AKAMAI-ASN1 Akama... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
realtimeconversion
Show response
insight.adsrvr.org/track/ |
36 B 349 B |
87ms
63ms |
XHR
application/json |
52.223.40.198 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
OPTIONS H2 |
200 |
realtimeconversion
insight.adsrvr.org/track/ Frame |
0 0 |
76ms
53ms |
Preflight
application/json |
52.223.40.198 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
realtimeconversion
Show response
insight.adsrvr.org/track/ |
36 B 350 B |
88ms
64ms |
XHR
application/json |
52.223.40.198 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
OPTIONS H2 |
200 |
realtimeconversion
insight.adsrvr.org/track/ Frame |
0 0 |
74ms
53ms |
Preflight
application/json |
52.223.40.198 Amazon.com |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||








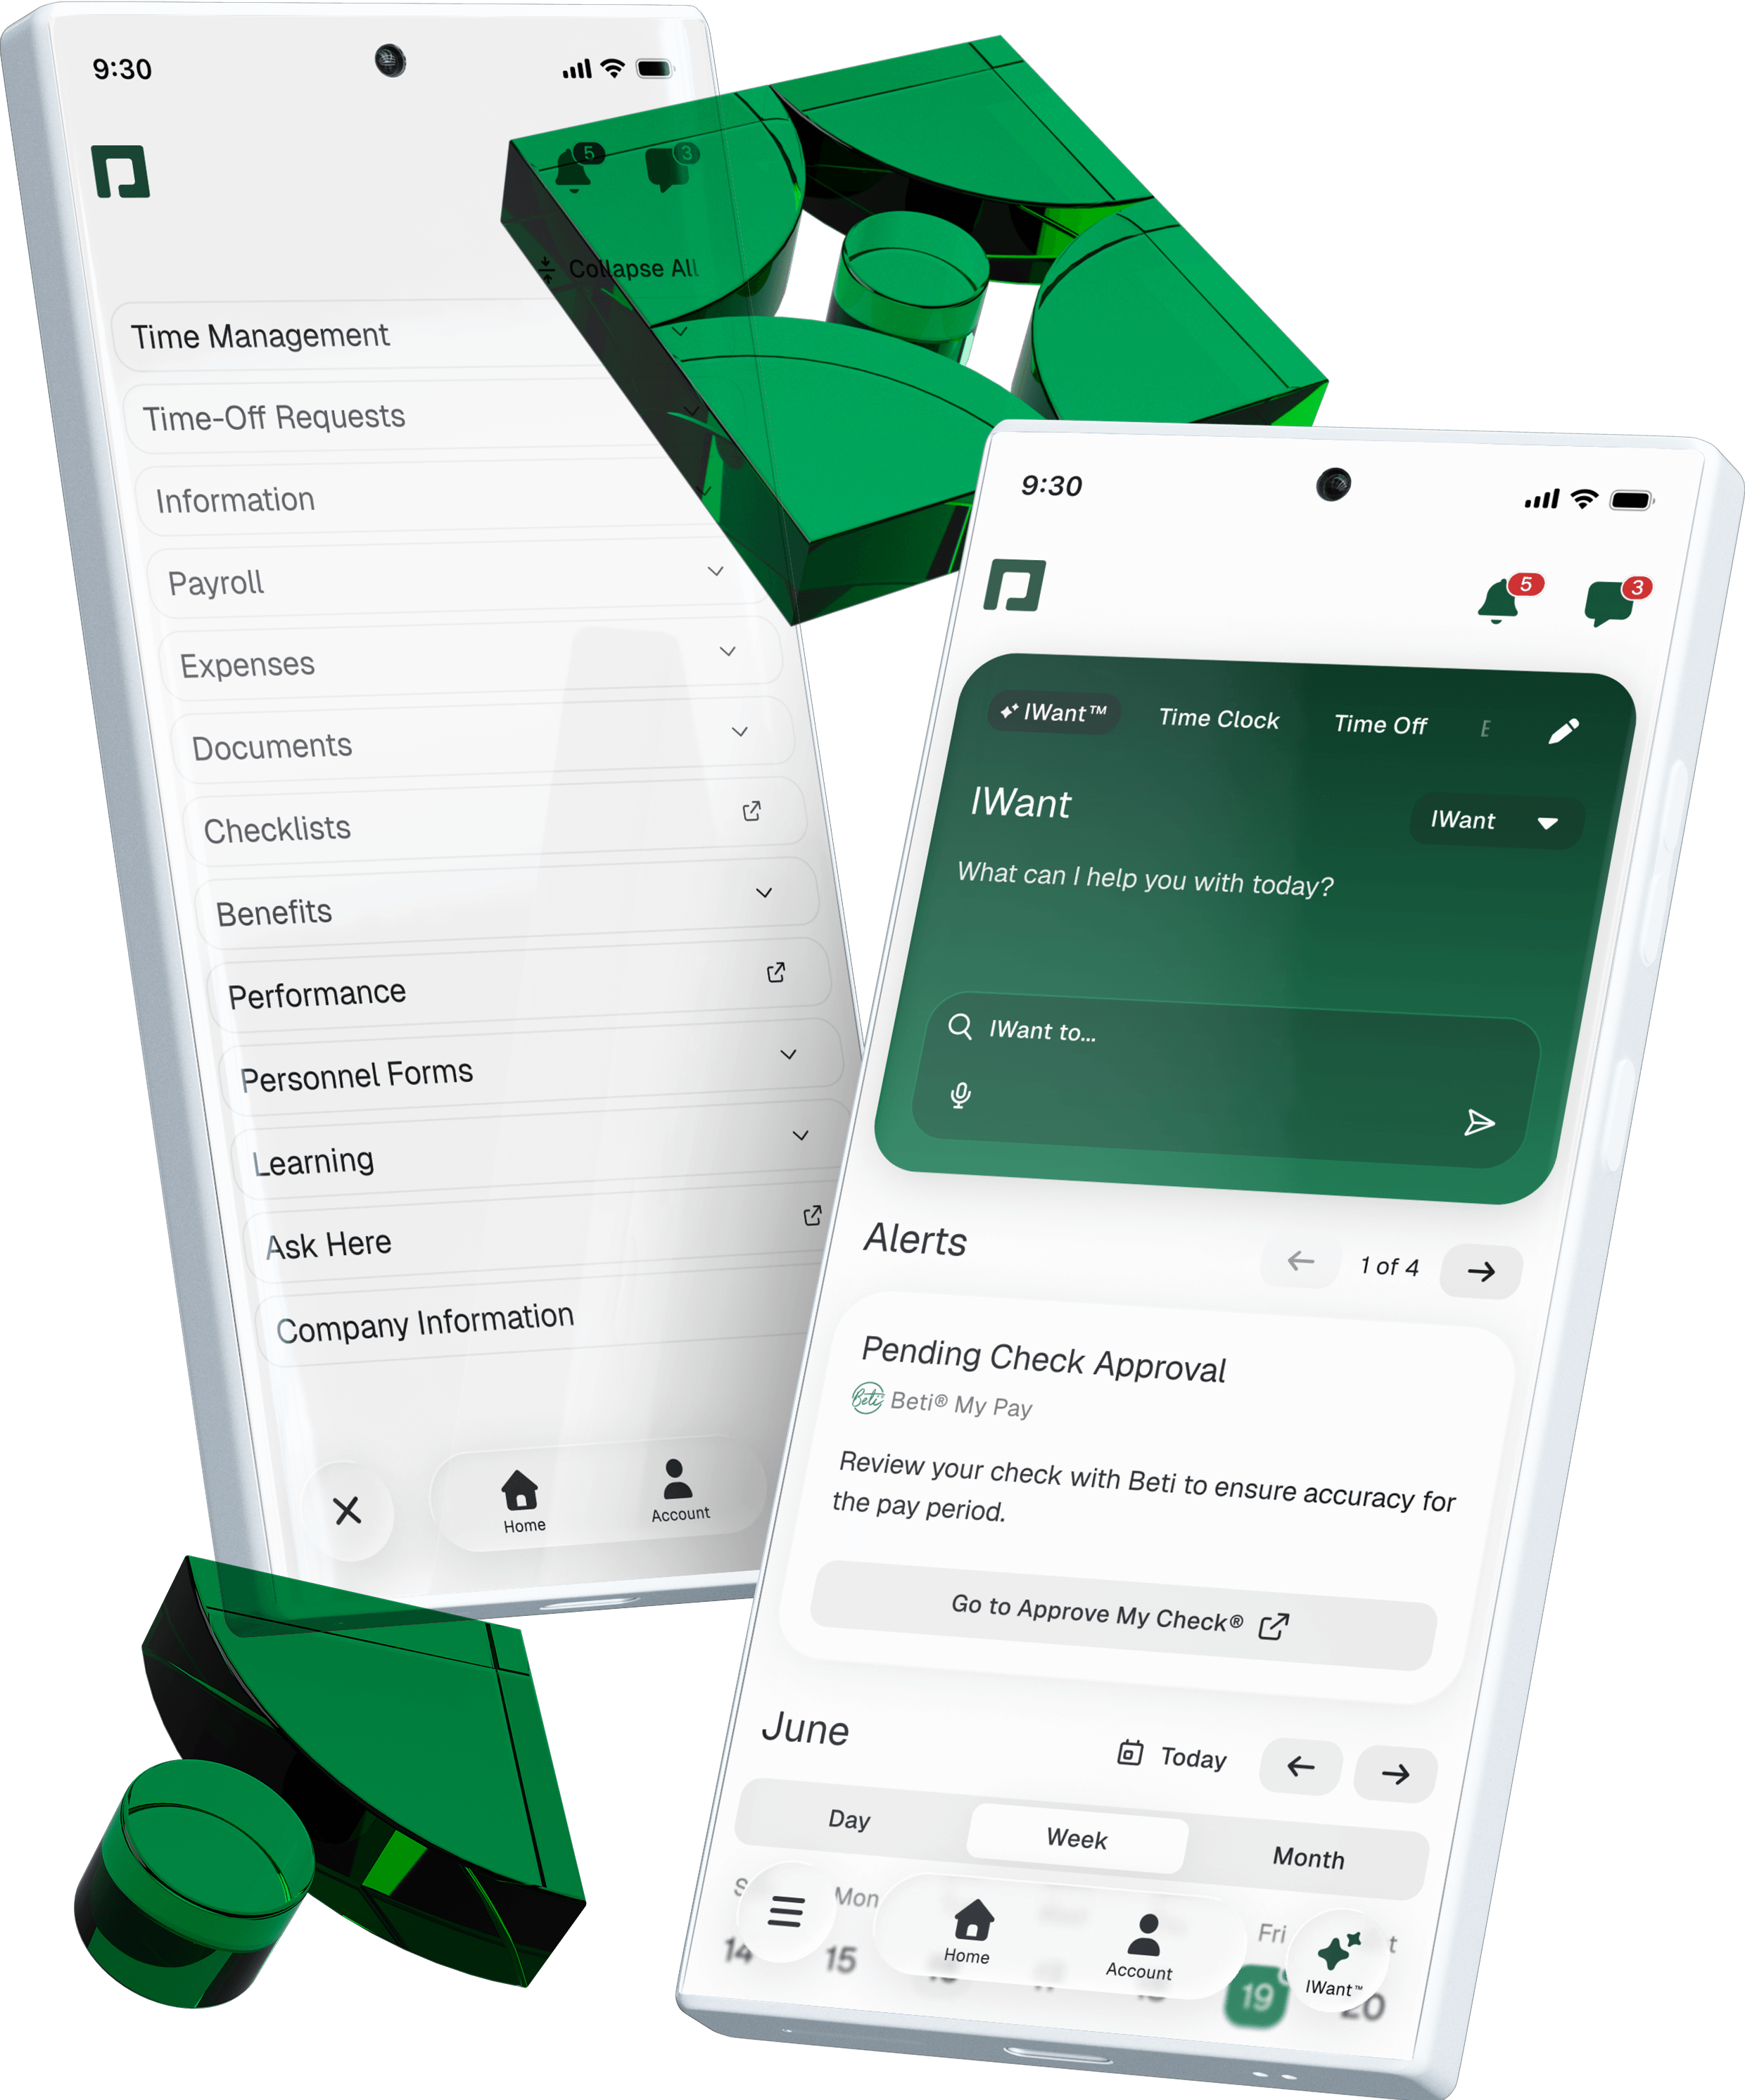


Failed requests
These URLs were requested, but there was no response received. You will also see them in the list above.
- Domain
- s.ml-attr.com
- URL
- https://s.ml-attr.com/getuid?https%3a%2f%2fattr.ml-api.io%2f%3fdomain%3dpaycom.com%26pId%3d%24UID
Verdicts & Comments Add Verdict or Comment
106 JavaScript Window variables
Go Pro
Only in urlscan Pro
Inspect and pivot on JavaScript variables, identifiers, and other key site metadata data with urlscan Pro. Reveal and search on client-side frameworks, runtime variables, and custom values.
Click for more information
Free trials of urlscan Pro are available.
These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.
object| 0 object| 1 object| 2 object| 3 function| $ function| jQuery object| pcHttpBlockTests object| pcDatalayer object| OneTrustStub object| dataLayer object| OtTrustedType object| $form string| footerFormType object| loadingGifFooter object| algoliasearch object| @algolia/autocomplete-js object| @algolia/autocomplete-plugin-query-suggestions object| CookieBanner object| vidyardEmbed function| setImmediate function| clearImmediate boolean| __vidyardParentOriginListening object| VidyardV4 object| Vidyard boolean| tickerJSLoaded function| cleanRenderedText function| demo function| closeDemo object| gbResourceTile number| gbHeaderHeight number| blogNavHeight number| mobileNavHeight function| externalAnchorScroll function| smoothScrollToAnchor object| pcUserCookies object| paycomUtilityJS object| bootstrap function| onVidyardAPI string| OnetrustActiveGroups string| OptanonActiveGroups object| otStubData string| tickerValueSelector string| tickerValueContainer string| AlgoliaAnalyticsObject function| aa object| _listeners object| google_tag_manager object| google_tag_data object| AlgoliaAnalytics object| Optanon object| OneTrust function| twq string| _linkedin_data_partner_id string| TiktokAnalyticsObject object| ttq function| fbq function| _fbq object| zi string| ZIProjectKey string| STYLE_ID object| style string| SLScoutObject function| slscout function| gtag object| GooglebQhCsO object| TTDConversionEvents object| ttdConversionEventsLayer object| ttdConversionEvents function| ttd_dom_ready function| TTDUniversalPixelApi object| ttd_up_api function| loadZILogs function| errorHandler string| TAG_VERSION function| _sendTelemetry object| saved function| getIframeWrapperForm function| findEl object| zitag object| ZILogs function| mktoMunchkinFunction object| Munchkin function| mktoMunchkin object| twttr function| UET function| UET_init function| UET_push object| ueto_b7f1bcb4a9 object| uetq function| podscribe string| podscribe_user_id string| podscribe_advertiser string| cookie function| onYouTubeIframeAPIReady object| gaGlobal object| _zi_fc function| lintrk boolean| _already_called_lintrk object| MunchkinTracker function| webinsights object| insightsuetq object| _ziziws object| ziws object| regeneratorRuntime object| _zi object| ORIBILI57 Cookies
Go Pro
Only in urlscan Pro
Review, search, and pivot on browser cookies and persistence site data to see how a site tracks users and keeps sessions alive across visits.
Click for more information
Free trials of urlscan Pro are available.
Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.
| Domain/Path | Expires | Name / Value | |||
|---|---|---|---|---|---|
| test-app.rpspayroll.org/ | 1970-01-21 17:36:01 |
Name: cookie_secure_5min Value: !u/rwwHxgJJ+NnDf+NqpaRKIv2mTVHpKUpgNjbBhAKJaUcHgX85sru7dmwC4Kx02IQSG7CbrN/g== |
|||
| test-app.rpspayroll.org/ | 1969-12-31 23:59:59 |
Name: TS01ad0fe2 Value: 014586c95ad52e56e66efae2a66fe9d182a2ea92f55e59bfda8d534c0fd560f4ecea00565a7a7f005c512564d36f05d3f6a1b887dc |
|||
| www.paycom.com/ | 1969-12-31 23:59:59 |
Name: pcIsGeoFenced Value: false |
|||
| .paycom.com/ | 1970-01-21 19:45:37 |
Name: _gcl_au Value: 1.1.2096428723.1791361338 |
|||
| .g2crowd.com/ | 1970-01-21 17:36:03 |
Name: __cf_bm Value: bn4HPSI07c88XMU0t_lSh77luGc9H7oYWYznAGXucyY-1791361338.1003702-1.0.1.1-Q3GwJ.PIH7Tnom4aITNX4lm4YkWl27RUrzx7OLqnV2CYUTJ1503LrjCdVYOKAPa0xl8naTjmniqXdGOLCM2hnklvnbbI78VG20DIAE.TolL.TlSyuD_uNZ9Tez6yxkNf |
|||
| .tiktok.com/ | 1970-01-22 02:57:37 |
Name: _ttp Value: 3KMJ7op9foHupqIGImC0GGMNnzi.1791361338146 |
|||
| .paycom.com/ | 1970-01-22 02:21:37 |
Name: OptanonConsent Value: isGpcEnabled=0&datestamp=Tue+Oct+06+2026+22%3A22%3A18+GMT-1000+(Hawaii-Aleutian+Standard+Time)&version=202510.2.0&browserGpcFlag=0&isIABGlobal=false&hosts=&consentId=c63a65ed-5e1c-4dbc-be00-466433627767&interactionCount=0&isAnonUser=1&landingPath=https%3A%2F%2Fwww.paycom.com%2F&groups=1%3A1%2C3%3A1%2CSSPD_BG%3A1%2C2%3A1%2C4%3A1%2C8%3A1 |
|||
| .paycom.com/ | 1970-01-22 02:57:37 |
Name: _twsid Value: 1791361338321-819825658.1.1791361338321 |
|||
| .paycom.com/ | 1970-01-22 02:57:37 |
Name: _twpid Value: tw.1791361338321.526210856456516447 |
|||
| .paycom.com/ | 1970-01-22 02:21:37 |
Name: __ps_r Value: _ |
|||
| .paycom.com/ | 1970-01-21 17:36:03 |
Name: __ps_sr Value: _ |
|||
| .paycom.com/ | 1970-01-22 02:21:37 |
Name: __ps_lu Value: https://www.paycom.com/ |
|||
| .paycom.com/ | 1970-01-21 17:36:03 |
Name: __ps_slu Value: https://www.paycom.com/ |
|||
| .paycom.com/ | 1970-01-22 02:21:37 |
Name: __ps_did Value: pscrb_ee15f323-954d-487b-9380-cb6fee563165 |
|||
| .paycom.com/ | 1970-01-22 02:21:37 |
Name: __ps_fva Value: 1791361338348 |
|||
| .adsrvr.org/ | 1970-01-22 02:21:37 |
Name: TDID Value: 4333c6f4-5603-4421-9023-4dce73762881 |
|||
| .t.co/ | 1970-01-22 03:12:01 |
Name: muc_ads Value: 35fb5104-b8fe-43b5-839b-d5c946dd1906 |
|||
| .t.co/ | 1970-01-21 17:36:03 |
Name: __cf_bm Value: W1JLNXrAyTZXK02Mg2XBmamNphP8ZGZhAcFfA0Cq6zs-1791361338.3797984-1.0.1.1-Ohfk5hrSAhvpC5NsDY2oyVsAYe10hGopyLdtmEB.AT2y0u8rKsXYQCG41i8IjBh3q3Cn_u7him_seGZjxGGjxbjhQsdwGj2Bk0_ELDPw5cwzv30ynUmsjNkC8M2.GpUp |
|||
| .twitter.com/ | 1970-01-22 03:12:01 |
Name: personalization_id Value: "v1_ui1NaBX3O+ww6/F/4jOILg==" |
|||
| .twitter.com/ | 1970-01-21 17:36:03 |
Name: __cf_bm Value: i_mhH1xZX8HZ4lBj9NFIh4GKghtLDwiZfMMH2dtozb8-1791361338.3874664-1.0.1.1-Wv.0szYbafSXkvgFXUl4DuWWtT8eKS.uK9avUxig4iK2SNWGxWzX1J5caTHlOrsM1JKjijScgwbKUNakeRVIE8.inD2mTqNnOYOkgIjQNsbXFZbudPOkdJvLqMx14kSe |
|||
| .g2.com/ | 1970-01-21 17:36:03 |
Name: __cf_bm Value: wfrVwflmBwf9Vof6BxFDa8fjfk3YRqD2mVAID1y3s48-1791361338.455165-1.0.1.1-s8uAtFVmhdMLmG3Cwadd7ZX3MD..e5rGE3rnrDo.HYJY.0oq0R_beiVERdm3gBypbx5e0XLItaWC1NuDG8STk.H6og2XfcZjk8HhQObpKZLGODDlyaHNZdzcyK7XyRCz |
|||
| .paycom.com/ | 1970-01-22 03:12:01 |
Name: _ga_28LCM29C6P Value: GS2.1.s1791361338$o1$g0$t1791361338$j60$l0$h0 |
|||
| .paycom.com/ | 1970-01-22 03:12:01 |
Name: _ga Value: GA1.1.1030115391.1791361339 |
|||
| .www.paycom.com/ | 1970-01-22 02:21:37 |
Name: _zitok Value: 9522c650ca98e8f0d6471791361338 |
|||
| .paycom.com/ | 1970-01-22 03:12:01 |
Name: _mkto_trk Value: id:502-GZQ-487&token:_mch-paycom.com-e92ee9b843285328527d23b39f227647 |
|||
| .bing.com/ | 1970-01-22 02:57:37 |
Name: MUID Value: 284CAA1B15226CBD0700BDF014616DE6 |
|||
| .bat.bing.com/ | 1970-01-21 17:46:06 |
Name: MR Value: 0 |
|||
| .rubiconproject.com/ | 1970-01-22 02:21:37 |
Name: audit_p Value: 1|VOYFyIrzzZJerJKoJGAnjAXxTBzL5w7xy3cXPvuXXxRE+urrj8AHNyT2dnM4DS5ifEtnApw1BgiM1KxoLazIt9i2Wk5FrGos0XY24Ec+XLuwkc5wqvQCd29NjnQ/CikeOzslGipookupZTWq2asVLBlhOLxHL+Z9OpWvBGztqNVbOz6AjJtUa8ZnH3r7x5VAdeodiyl5GGjkt77VmXBK7kiCfUmSYXqD+ohH/uuQN8oOr/S07bYDcYQkZmofZQkSVSwKu1RXSJT0/fhu8/pkBO4VeIulq+4M1TRwmTZWV3Xc6UO785F0Pw== |
|||
| .rubiconproject.com/ | 1970-01-22 02:21:37 |
Name: khaos Value: MUXUAF3T-E-6EZ7 |
|||
| .rubiconproject.com/ | 1970-01-22 02:21:37 |
Name: khaos_p Value: MUXUAF3T-E-6EZ7 |
|||
| .rubiconproject.com/ | 1970-01-22 02:21:37 |
Name: audit Value: 1|VOYFyIrzzZJerJKoJGAnjAXxTBzL5w7xy3cXPvuXXxRE+urrj8AHNyT2dnM4DS5ifEtnApw1BgiM1KxoLazIt9i2Wk5FrGos0XY24Ec+XLuwkc5wqvQCd29NjnQ/CikeOzslGipookupZTWq2asVLBlhOLxHL+Z9OpWvBGztqNVbOz6AjJtUa8ZnH3r7x5VAdeodiyl5GGjkt77VmXBK7kiCfUmSYXqD+ohH/uuQN8oOr/S07bYDcYQkZmofZQkSVSwKu1RXSJT0/fhu8/pkBO4VeIulq+4M1TRwmTZWV3Xc6UO785F0Pw== |
|||
| .paycom.com/ | 1970-01-21 19:45:37 |
Name: _fbp Value: fb.1.1791361338630.462902988122471256 |
|||
| .doubleclick.net/ | 1970-01-22 03:12:01 |
Name: IDE Value: AHWqTUmpFSgYoH5g6drcfNZtx-T-pTXnQiZiudw9oLxbvu5yAOhmmEHQL3hVADr92Nk |
|||
| .demdex.net/ | 1970-01-21 21:55:13 |
Name: demdex Value: 71039970736592401367024527516577174148 |
|||
| .dpm.demdex.net/ | 1970-01-21 21:55:13 |
Name: dpm Value: 71039970736592401367024527516577174148 |
|||
| .facebook.com/ | 1970-01-21 19:45:37 |
Name: fr Value: 0TtX7NRmjm7Cvup4e..BqxgE6...1.0.BqxgE6.AWeWpFld6vmxZWN-JWH_B8uff6E |
|||
| www.paycom.com/ | 1970-01-21 17:46:06 |
Name: slireg Value: https://scout.us4.salesloft.com |
|||
| .linkedin.com/ | 1970-01-21 19:45:37 |
Name: li_sugr Value: 88747305-fbf0-45f3-8900-082fbcd69f2e |
|||
| .linkedin.com/ | 1970-01-22 02:21:37 |
Name: bcookie Value: "v=2&33ef0ad1-1839-4a16-8d52-b24c782bc803" |
|||
| .linkedin.com/ | 1970-01-21 17:37:27 |
Name: lidc Value: "b=OGST00:s=O:r=O:a=O:p=O:g=3963:u=1:x=1:i=1791361338:t=1791447738:v=2:sig=AQHUsutdlBA_CkhDyP3Gnm5QyE5rZZSU" |
|||
| .linkedin.com/ | 1970-01-21 17:36:03 |
Name: __cf_bm Value: hdMjuTHjcN2V.FE9WLoiM0pTl3647h4EXSRmJjsqKv4-1791361338.615531-1.0.1.1-QMa3jkBKnBFhV9COxsGudEprDj1wKZw83YB9vXsIXWf.23zKICfFEisy5ZSirkBrSBaOiY8bFUEVe8g0C9XZ3TlfuL.EvzmnCV7TKl765tK5RuLbMNUpqQzQzri7x8zj |
|||
| .adnxs.com/ | 1970-01-21 19:45:37 |
Name: XANDR_PANID Value: anL2_42zA_Hs0e6Jh5hIQgMOznyarVFSKaSPQZRdjhlj478rynzOSj5flC_wd5w3bZYD9IfnYlYW9tmgfRkgUpukPK7qiU5L-RKHSUbiEFw. |
|||
| .adnxs.com/ | 1970-01-21 19:45:37 |
Name: uuid2 Value: 3896039076974146054 |
|||
| .zoominfo.com/ | 1969-12-31 23:59:59 |
Name: _cfuvid Value: 8qktXPn4SB0RLn28ukPn2OLCGnhIG7SWKOF0TEV_.Io-1791361338.6583362-1.0.1.1-Jgduh6QOYXKDtDuvcQPz8i.0cE4l6lCy_z_qw_KPHeE |
|||
| .adsrvr.org/ | 1970-01-22 02:21:37 |
Name: TDCPM Value: CAESFwoIYXBwbmV4dXMSCwjetNSpxJXSPxAFEhUKBmdvb2dsZRILCOq04qjEldI_EAUSFgoHcnViaWNvbhILCOzD6qbEldI_EAUYBSAEKAYyCwis1ezT2pXSPxAFWgdjZ3djdXJ1YAF6CQoFdGllcjIQAQ.. |
|||
| .paycom.com/ | 1970-01-22 02:57:37 |
Name: _tt_enable_cookie Value: 1 |
|||
| .paycom.com/ | 1970-01-22 02:57:37 |
Name: _ttp Value: 01M4AQ9KC4C5PNZY2A9DMYHERB_.tt.1.1791361338757 |
|||
| www.paycom.com/ | 1970-01-22 02:21:37 |
Name: sliguid Value: 0de10545-c9a9-4060-88d1-455794b64c09 |
|||
| www.paycom.com/ | 1970-01-22 02:21:37 |
Name: slirequested Value: true |
|||
| .linkedin.com/ | 1970-01-21 18:19:13 |
Name: UserMatchHistory Value: AQIFgiASbeIyTwAAAaEVdM3WZyCJP9IaYplovioNnPZlhrI9qr7SMmqpvzOqHR-IKIyQooYUfPEt-w |
|||
| .linkedin.com/ | 1970-01-21 18:19:13 |
Name: AnalyticsSyncHistory Value: AQIIBPk3AJMdOgAAAaEVdM3Wro-UAX6ygR1KySAbUuuai6bPPau7NpdTx0jfFLXXSCXjt1c3HvQQsowfDBDLbw |
|||
| .paycom.com/ | 1970-01-21 17:37:27 |
Name: _uetsid Value: 3603c6b0c22811f1bb31174ab5cc600f|1utvyg1|2|ga3|0|2471 |
|||
| .www.linkedin.com/ | 1970-01-22 02:21:37 |
Name: bscookie Value: "v=1&20261007082218860ea7af-6765-4b6e-86f8-01630e58faa9AQGu7dGFB6ixezLOsHMBrp2bNCIj0eih" |
|||
| .paycom.com/ | 1970-01-22 02:57:37 |
Name: _uetvid Value: 3603f680c22811f183f4655bb3aa00d6|i11kjn|1791361339057|1|1|bat.bing.com/p/conversions/c/z |
|||
| .paycom.com/ | 1970-01-22 02:57:37 |
Name: ttcsid Value: 1791361338766::V1RU5mVyoiIkrenLVUvG.1.1791361339120.0::1.-3090.0::0.0.0.0::0.0.0 |
|||
| .paycom.com/ | 1970-01-22 02:57:37 |
Name: ttcsid_C7O68OTTSIPDF1VI94SG Value: 1791361338766::tNPHISzvsxhRq1zpPz-w.1.1791361339120.0 |
|||
| .paycom.com/ | 1970-01-22 02:57:37 |
Name: ttcsid_CGGVI7BC77UF41IP8370 Value: 1791361338767::p5JauME-lho20p_aBfss.1.1791361339120.0 |
Security Headers
This page lists any security headers set by the main page. If you want to understand what these mean and how to use them, head on over to this page
| Header | Value |
|---|---|
| Content-Security-Policy | default-src 'self' *.vidyard.com *.onetrust.com *.zi-scripts.com *.salesloft.com; frame-ancestors 'self'; form-action *; object-src 'none'; base-uri 'none'; style-src * 'unsafe-inline'; script-src * 'unsafe-inline' 'unsafe-eval' blob:; img-src * 'unsafe-inline' 'unsafe-eval' data: blob:; connect-src *; worker-src * blob:; frame-src * blob:; font-src * data:; media-src * blob:; |
| Strict-Transport-Security | max-age=31536000 |
| X-Content-Type-Options | nosniff |
Indicators
This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.
15036603.fls.doubleclick.net
502-gzq-487.mktoresp.com
ad.doubleclick.net
adservice.google.com
analytics-ipv6.tiktokw.us
analytics.google.com
analytics.tiktok.com
analytics.twitter.com
b.videoamp.com
bat.bing.com
cdn.cookielaw.org
cdn.jsdelivr.net
cdn.paycom.com
cdn.vidyard.com
cm.g.doubleclick.net
connect.facebook.net
d34r8q7sht0t9k.cloudfront.net
dpm.demdex.net
geolocation.onetrust.com
googleads.g.doubleclick.net
ib.adnxs.com
insight.adsrvr.org
ipv4.podscribe.com
js.adsrvr.org
js.zi-scripts.com
match.adsrvr.org
munchkin.marketo.net
pixel.rubiconproject.com
play.vidyard.com
px.ads.linkedin.com
s.ml-attr.com
scout-cdn.salesloft.com
scout.salesloft.com
snap.licdn.com
static.ads-twitter.com
stats.g.doubleclick.net
t.co
test-app.rpspayroll.org
tracking-api.g2.com
tracking.g2crowd.com
verifi.podscribe.com
ws-assets.zoominfo.com
ws.zoominfo.com
www.facebook.com
www.google.com
www.googletagmanager.com
www.linkedin.com
www.paycom.com
www.paycomonline.com
s.ml-attr.com
104.16.118.43
104.16.188.41
104.17.207.5
104.18.30.176
104.18.32.137
104.18.37.212
104.18.87.42
104.19.164.102
107.162.254.104
13.223.123.134
13.226.103.193
13.32.241.107
13.32.241.20
13.33.67.105
142.250.191.8
142.250.217.134
142.250.65.66
142.250.68.194
142.251.153.119
142.251.41.162
142.251.45.198
142.251.45.206
146.75.28.157
150.171.28.10
151.101.65.181
162.159.140.229
172.253.62.157
172.64.146.215
172.66.0.227
192.28.164.179
216.19.192.2
216.226.2.26
23.13.173.12
23.200.3.22
23.219.161.114
23.40.18.49
23.49.248.11
3.228.126.156
3.33.220.150
32.192.128.18
34.21.100.80
35.170.37.64
52.223.40.198
57.144.180.1
57.144.180.128
68.67.160.75
035a78c33f34bc46878df7e9b94506ace53231e679010c0f1423d518ae979b41
06d0f328278a6bb9582c4008bb1edad18d994ba4f903c1a69bde69636ec62b80
0bd3649aeae20f4bb708864b8e40a446e3cca57f410de95d2834bf881034922b
0c6c2e000901250ef3fc11bd23c90ba0274b3766a121fa7d62332200c151a918
0c7178cc6ca34fb18e30f070a5e7a1c287b2d7ccfcba2cfdf06e0f46eda55740
0facedbd8f25d3316a169d0504bd79e6e35052e76bd9a01e3aa2654e09ca51b1
13123b0775f99763f62b9a6a6ab240c7cf867b3bef7c0be3fce77a8ab3a4c871
14a79518f1e5fa0ee04e788884131b4ccb855f90123a02027773c68ae4c46e52
15a3dc247a9802298e21568c4d7d501a6236c246e9a2257177799a5400844740
1e05381160d3bc508aae36ca5a6f0ade2d359ebd1f3d2a051b7c6de6b151bba7
2094a328992aaac2089986e18c69387b9a2a30103278af5504a27e1123b2d0d0
24cfc62617730b3061cefacc0687b533fc0b542f2379c82f47ac37233977d832
255d095e1ffdc048a732481381219d3e2a8d3d64ab9fb16074215666adb02cdf
25c01e14264e1b1425b9f1a6264cc5470743b67119fa08adcaf95e8fdff7ce91
2b469efee624abffe66bcb1ec6f58a1a223114ba5d7cdd0e71c37955ce923e15
2fd60f2b5eccb2d2d08f78aacff09b4297043b0d981ed637f8812e0e5e3ecf69
30dadeaf451e7bc8e280eb2b2a36d0ef793112caa71ce20de14f07d8ac1fe9b5
34d3b33f43065334fe91b07e3ee7f05c9763d6cd96b45a033bf85ef485df5267
36410f6eb340de22576616daedf209e6283bd26640e5cac4ab8df6d13f2b76ec
3902a2fbbbe5f0209bc63ac1a0f2a51d51010c7deae2d9ea91184edc8867ba0d
39cd4d973e0659c667748fff603aff547561a93452b0345e13075f28a5243dae
3a2163f66975c6987c6782c68c0680092ebc54c5c02243cf8621649e97ec6765
3a8a84275a9dfcc39df63405d1fb70f1a1180e6aab122f2252c8c927b402d090
3b1f2f6977a0487a38e537fb7d1fb6df4f1a9ab9774e0dd4f1af0d92fb12ec1e
4154825a6082bd5e8401da0328816618df3ed07de0d76c2a3aa41561b3a678b3
417c2fa4ff8cf5e36b1797c558e99b797cf8e9a960ce8e126ccd8de6ff09efca
4a007af67f716c30c8848ab0ad0bfaab8a5fcf3e36dedf918b59c9429d522440
4bebc12694755bc5edf1d849783992c7d470db7ede2b9cc74fa2dfd246c20aa1
4e1fa8d5b827735411373bc7551eecfaed72b57001b00b8da8edc34e32f4a033
4f53cda18c2baa0c0354bb5f9a3ecbe5ed12ab4d8e11ba873c2f11161202b945
5277b785c188393b28233eb0ac53955a21b0a1946762dc5335984f0993b38912
565339bc4d33d72817b583024112eb7f5cdf3e5eef0252d6ec1b9c9a94e12bb3
565f20d9dbef4f9616c6601edde302167ab5e081f9118d5a1567d64b38882fc3
586ff661fafa609cdf00c0df9586d9bbd2aa4087b02428dc02c4687ea3a75ab3
5a18450c5928df9c4c280dfa55761f6620cb96aba3cfe493a7f45e2cd85e6415
5e64a9d4392d3d29a3efdef5cf84a835b14661ebe8d92650b93038b4735e10ed
604bb787ab05f4bcab79d8e88c0372112e20d0ba47d834ef9c2c65ca2278741f
656c44454cc36f7cb8722f4d7208d3fac47808cb0ca64d629f8f90cecab538e3
66907191e2befaf2e1e29ba4b6061db28ece17499e32345fbb23df562cf02d87
691dcdb24853a0f5ce4e6597e5713dea66799b57ffe2c2a10f28f98e0b569b19
6a1d73995aada3cf1e81d5796ce6dbdae09a902641b58eea53fa4d12fca13c49
6bc1682958a81742b334a9936855cc117b0e7a686d25b6194c5622c32dbe3ec6
6c89911b13aba46daec3118dc89c4f7f7eb7cf51a559db90fc6bcedb94318a7c
6cbd559e133b172823f3cd800bff272e0d3dc7969275debdc7b6152368efac66
6f0ca885e75af2465be650add088c06aa051385af0b975e9d5a13099ffd2f6ec
6f804517d6141cd19c7ee1f95d38a0704318221141f87ad20f998f6883741f83
746c7d0b4f28bb14a7dcba7522f3711566cda79a749ad619c9edb534d157927d
74df6a6e6baba23c158bc44b03c0e68cd743edffbf10942864e70e1414936b48
77841c951e8c2f578cfeab5c116f96fff5c257549190b79be69906b9b3a9b669
7b24e7fa864bdfde18260a08f2d508886c32ffb3b2db562dc081363f9841e51d
7c14da6e4101dcdbcc5f17e41dd9a1f2c9755f500ceedc85f60d09214c976962
7c549dad313b677b15cb870dc18f00ddc3a7aa549f53aa09dfdacd5db4d9e2da
828f63ab24ab5adcbfa9cca48e8be096c46f76d048b86b49f29f89f7b2997462
85a9f541a8f744d874bae555f1b61aca1e3a92848d9384c9d97749d91a323d59
886c86112a804ef1ddd1cb206af4c8c40e34b73c26652ca231404aa35a6b30d9
8968e2907b8936778ed050dd55d8ef7232b3d32ee95b1f7122b4dfa9e22c4839
8acd06258e9e7ff59374b350cea34bb5cd373dc6e6e5b8e768f7265f489ed850
8b1b6456e1893433673d3652e415f5336db9f5cd82843e4fa8e315ca665a618b
8d70b3e6badb6973663b398d297bb32eaedd08826a1af98d0a1cfce5324ffce0
905d1c432713432dca35dac3394abfaba23159d69f29eebfb3a6e73b33d0e975
94a56349b34c96fa1a81f9b72e1dcfffaa56a36f9e3ef620962db79e268f05f9
99b1ccefb730a82acf42a81d2503d85054938c61a6c435c565a2ddb1093eb8f0
9a3a77e97cab3a0fe0cc4f7b97f9e6d89672fe10a38d897f98a1503e80c7ceea
9adc1f5078410b97b403f636332c2f6e7b59300f361752bb81f1ecf5f8218972
9cbbf255dacf255e833c05b160728d890148725f0fc68b81f80a933cb876a81b
a08a4fef57e141da912d6cac009a0dda2ea9bf029b7dec9e245e727f1c779532
a5d1c9dd7ee8e087fc7f1e37fbe63f8299e702070ddd5d6b9345809a7c68f16f
a85866392118d4e9d6474f16c8d3654b039859e2085d6c01785129fd21422eb4
a879783358cd6f4aeab3f7be9a1d4bcad74e2ed414f7d6abcd60831f726e088a
a9dc2c582a6eee9bb8658db6b811ecafa9e353ad9d85199aefe147d440dd8009
aab6a662df923c04739f37c6a6d7f13fb91c8e3c6addd82fd5a6959e6f6241fb
ab588e5cbd3da66922b4ab44256fdf9f59e41c2fcbd2495e58638294c6447e02
ab790ca1212f73feba39a29265aeff9afd61ed6f4e91c986bf0dfe4900ef95e0
ac8778041fdb7f2e08ceb574c9a766247ea26f1a7d90fa854c4efcf4b361a957
ae9cd4f54b580f329bca81020d7b23b7bbd5520728da83b3a33069d0a552e82c
b0303de5b9bd20e99cc0b5d546974118fc9f215605cf0132ada27aeb13230ea9
b16b589e927d4804194dd9d3c6221db61e273a5a25ed2c002b7db96eeff28551
b37678e2c4e8452e51ee8902e176d670941b72bc06eaeeb951360f96322c6921
b8e18867e32b4d77c5000ed657f26a5c26bbdb283ab87f5e4101d73fcd38b5d3
bbdb0a56c8eb30d3b915526ca2bf873b4f73b05bb06be0ba790c9006abeb44fc
bcdaf127b041074c5c247242f8cf595009683d227b81fd6d7362f3f62d67f9ec
bedb81d0dc4ddbaa38e4bc26b8f6d09d97811d690dacb81c6c4f80cdc4bf208e
bf6bb5c768f5ff7c2ad5e80e478e90c426b508be13733bcfcd466237323b4f2d
c01cc4d5a2ced632fe4ed9e53b5e47919211972743f04745d4002ccc2565c59b
c37f5f759043a2b92dd2bde43ac254251b1c4544dbfd79cbc758fa513be55774
c417d61d7ec10c6cdee008c3912ce23b5584b3a0396aa2d418daf06206dab55e
cbdf0712673ad94781b25c743f49d8d6135f59d76ec1c9e060b4b2e259aeb28d
cbfcd76268acdf0645151132050d897f3bb91a41602bfdf8343b933694e843b5
ccbbec544e8761ea82e215145a3ab61e87f9f3869f9fa581f211bf34582d5d14
cddd450a33be5e50d6f27aea78d2e278beae2762678b22fc2dcee8de29cbc0be
cfb534cb19a532b3f0503dd1e354292f979b329125edaa72677492a3679cf2df
d14d81c474455f4fdfdbd5fa0976088226538f770ce8b99e6b95a0de387258fc
d28078950972ac2362ffb97c80d2ba6021febe2cc4ffcf174dfa4beef6acf69e
d28944b8805a165979a78a302e1109041c83a18da5f6aeb4bb64302f28e0bdf7
d39fc7f300cfc411b47e953c8b71dc4f9f16345b345f811f02edc282397f5b86
d8f9afbf492e4c139e9d2bcb9ba6ef7c14921eb509fb703bc7a3f911b774eff8
d985186cf725877de9c32f6b6d71c1f8e66c48d2ffd2a02ce62cb2d3f637a743
dcb09186a3d016b8ae56ecd0cb76f787254388177fc8318061d619b56a7d81b2
de1e399b07289f3b0a8d35142e363e128124a1185770e214e25e58030dad48e5
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
e3cdccecce813accca810dfb966557c7c9d74a49e165f8472f26d33abec8571e
e3ebd5ace0faa335d666bb88fa4a99cce3064e58d97ec06245b5c22500e523f0
e4274c084a88c8f00560c89fb521cb6918ca0b7170ce22918bad87905662b160
e4d413226ae85b0eed38b62f21a8bcd6bac9632089a3a988797c5521c82f30fc
e5cf2f3ac403cec84c6c3e72f2ac54f946982742e952f67cb4ba5cafcabeec3d
e84dd99e1f764be94b321bedbba21e2286b904afece2d4dec7e2e983047209be
ea58c13b90f2208e740d68e1820bb7fb06469d95f7765f1ee345a9ab68e50ee1
ebb22e4e6fa4eb471cec19576ddcc588e6f47a7a5dafc371753d003ec82f72df
ec6aee190548186e59e94aac53320ef65c2e9a397fbcbb64964ac6377a17c983
ef1955ae757c8b966c83248350331bd3a30f658ced11f387f8ebf05ab3368629
f02f1e1b46ff5edcef899af39571985f7e57d780e79efd16e72a37b2b96eac1a
f2c1cd4d4271dc5663c36dfe3aabb325e50a6982335b5f8ff4e88160622fa83d
f3295fcf174ea490981143b518a0f3da851345679db19be12f1c2edc50f6fd58
f5870712ca75ae3934fdf4920bba7e9023e5856b5025df5a9e491699f4c9ba7c
faae6fc0aa94cc5bde5076647c817a23206096a1cbeda10d1c6f3d89d6163ed1
fbec5939441b2f5f08b6540b0f1953f3e286d05ff098575c17986dd09ae5eaf8
fc876dc99a51fcf38fd5967fe58d9c7db1f00bfddc41f3df1e55017e1e804b2d
ff934128c8db47cc897eca0e2ddf007db1ed638ed18a5696ed7bb6ecce47b899