
www.radiobalkanfox.com
172.67.146.243
Public Scan
Open in
urlscan Pro
https://www.radiobalkanfox.com/bivsi-agent-meghan-markle-odlicno-je-sto-ne-radim-s-njom/ 10yr old
Submission: On October 08 via api (October 8th 2026, 2:37:45 am UTC) from US — Scanned from IL Go Pro
Only in urlscan Pro
- Select different country locations for Private Scans.
- Use a global network of additional scanning locations and residential IPs for scanning.
- Interact with pages while you are scanning them.
- Download files from remote websites.
- Scan websites on the Tor Network.
Summary
TLS certificate: Issued by WE1 on September 2nd 2026. Valid for: 3mo.
This is the only time www.radiobalkanfox.com was scanned on urlscan.io!
urlscan.io Verdict: No classification
Domain & IP information
| IP Address | AS Autonomous System | ||
|---|---|---|---|
| 61 | 172.67.146.243 172.67.146.243 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 142.251.13.95 142.251.13.95 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 2 | 142.251.20.97 142.251.20.97 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 2 | 192.0.73.2 192.0.73.2 | 2635 (AUTOMATTIC) (AUTOMATTIC - Automattic) | |
| 41 | 157.240.0.6 157.240.0.6 | 32934 (FACEBOOK) (FACEBOOK - Facebook) | |
| 1 | 104.16.80.73 104.16.80.73 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 6 | 172.67.71.68 172.67.71.68 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 6 | 192.178.183.94 192.178.183.94 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 2 | 91.207.22.61 91.207.22.61 | 47948 (SATA-AS 2...) (SATA-AS 24sata doo) | |
| 2 | 142.251.151.4 142.251.151.4 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 5 | 57.144.244.1 57.144.244.1 | 32934 (FACEBOOK) (FACEBOOK - Facebook) | |
| 2 | 142.251.14.139 142.251.14.139 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 6 | 142.251.153.4 142.251.153.4 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 2 | 142.250.154.155 142.250.154.155 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 142.251.13.148 142.251.13.148 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 3 | 142.251.155.119 142.251.155.119 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 14 | 45.80.89.83 45.80.89.83 | 208905 (Exelera-A...) (Exelera-AS Exelera Telecom Ltd) | |
| 1 | 142.250.154.119 142.250.154.119 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 2 | 172.217.116.4 172.217.116.4 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 163 | 20 |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| www.radiobalkanfox.com 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: wt-in-f95.1e100.net
| fonts.googleapis.com 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: bx-in-f97.1e100.net
| www.googletagmanager.com 14yr old |
ASN2635 (AUTOMATTIC - Automattic, Inc, US)
| secure.gravatar.com 10yr old |
ASN32934 (FACEBOOK - Facebook, Inc., US)
PTR: xx-fbcdn-shv-02-fra3.fbcdn.net
| connect.facebook.net 14yr old | |
| static.xx.fbcdn.net 10yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| static.cloudflareinsights.com 7yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| cdn.buttonizer.io 5yr old | |
| api.buttonizer.io 5yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: lcfraw-in-f94.1e100.net
| fonts.gstatic.com 10yr old |
ASN32934 (FACEBOOK - Facebook, Inc., US)
PTR: edge-star-mini-shv-01-fra5.facebook.com
| www.facebook.com 12yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: pm-in-f139.1e100.net
| www.google-analytics.com 14yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: bt-in-f155.1e100.net
| googleads.g.doubleclick.net 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: wt-in-f148.1e100.net
| static.doubleclick.net 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
| www.google.com 14yr old | |
| www.youtube.com 10yr old |
ASN208905 (Exelera-AS Exelera Telecom Ltd, IL)
| scontent.ftlv21-1.fna.fbcdn.net 4yr old | |
| external.ftlv21-1.fna.fbcdn.net 2yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: bt-in-f119.1e100.net
| i.ytimg.com 10yr old |
| Apex Domain Subdomains |
Transfer | |
|---|---|---|
| 61 |
radiobalkanfox.com
www.radiobalkanfox.com 10yr old |
734 KB |
| 50 |
fbcdn.net
static.xx.fbcdn.net — Cisco Umbrella Rank: 873 10yr old scontent.ftlv21-1.fna.fbcdn.net — Cisco Umbrella Rank: 459095 4yr old external.ftlv21-1.fna.fbcdn.net 2yr old |
1 MB |
| 10 |
youtube.com
www.youtube.com — Cisco Umbrella Rank: 113 10yr old |
991 KB |
| 6 |
gstatic.com
fonts.gstatic.com — Cisco Umbrella Rank: 31 10yr old |
134 KB |
| 6 |
buttonizer.io
cdn.buttonizer.io — Cisco Umbrella Rank: 108493 5yr old api.buttonizer.io — Cisco Umbrella Rank: 112891 5yr old |
134 KB |
| 5 |
facebook.com
www.facebook.com — Cisco Umbrella Rank: 134 12yr old |
45 KB |
| 5 |
facebook.net
connect.facebook.net — Cisco Umbrella Rank: 225 14yr old |
297 KB |
| 3 |
doubleclick.net
1 redirects
googleads.g.doubleclick.net — Cisco Umbrella Rank: 68 10yr old static.doubleclick.net — Cisco Umbrella Rank: 283 10yr old |
664 B |
| 3 |
googleapis.com
fonts.googleapis.com — Cisco Umbrella Rank: 43 10yr old jnn-pa.googleapis.com — Cisco Umbrella Rank: 361 5yr old |
1 KB |
| 2 |
google-analytics.com
www.google-analytics.com — Cisco Umbrella Rank: 85 14yr old |
21 KB |
| 2 |
24sata.hr
img.24sata.hr — Cisco Umbrella Rank: 535724 6yr old |
27 KB |
| 2 |
gravatar.com
secure.gravatar.com — Cisco Umbrella Rank: 2314 10yr old |
18 KB |
| 2 |
googletagmanager.com
www.googletagmanager.com — Cisco Umbrella Rank: 45 14yr old |
286 KB |
| 1 |
ytimg.com
i.ytimg.com — Cisco Umbrella Rank: 126 10yr old |
2 KB |
| 1 |
google.com
www.google.com — Cisco Umbrella Rank: 3 14yr old |
24 KB |
| 1 |
cloudflareinsights.com
static.cloudflareinsights.com — Cisco Umbrella Rank: 303 7yr old |
10 KB |
| 0 |
qaquicky.com
Failed
ads.qaquicky.com Failed 4yr old |
|
| 163 | 17 |
| Domain | Requested by | |
|---|---|---|
| 61 | www.radiobalkanfox.com |
www.radiobalkanfox.com
static.cloudflareinsights.com |
| 36 | static.xx.fbcdn.net |
www.facebook.com
static.xx.fbcdn.net |
| 10 | external.ftlv21-1.fna.fbcdn.net |
www.facebook.com
|
| 10 | www.youtube.com |
www.radiobalkanfox.com
www.youtube.com |
| 6 | fonts.gstatic.com |
fonts.googleapis.com
www.youtube.com |
| 5 | www.facebook.com |
connect.facebook.net
www.radiobalkanfox.com static.xx.fbcdn.net |
| 5 | connect.facebook.net |
www.radiobalkanfox.com
connect.facebook.net |
| 4 | scontent.ftlv21-1.fna.fbcdn.net |
www.facebook.com
|
| 4 | cdn.buttonizer.io |
www.radiobalkanfox.com
cdn.buttonizer.io |
| 2 | jnn-pa.googleapis.com |
www.youtube.com
|
| 2 | googleads.g.doubleclick.net |
1 redirects
www.youtube.com
|
| 2 | api.buttonizer.io |
cdn.buttonizer.io
|
| 2 | www.google-analytics.com |
www.googletagmanager.com
|
| 2 | img.24sata.hr |
www.radiobalkanfox.com
|
| 2 | secure.gravatar.com |
www.radiobalkanfox.com
|
| 2 | www.googletagmanager.com |
www.radiobalkanfox.com
www.googletagmanager.com |
| 1 | i.ytimg.com |
www.youtube.com
|
| 1 | www.google.com |
www.youtube.com
|
| 1 | static.doubleclick.net |
www.youtube.com
|
| 1 | static.cloudflareinsights.com |
www.radiobalkanfox.com
|
| 1 | fonts.googleapis.com |
www.radiobalkanfox.com
|
| 0 | ads.qaquicky.com Failed |
www.radiobalkanfox.com
|
| 163 | 22 |
This site contains links to these domains. Also see Links.
| Domain |
|---|
| balkanfox.com |
| prvihosting.com |
| api.whatsapp.com |
| www.24sata.hr |
| www.thetimes.com |
| pagesix.com |
| www.youtube.com |
| m.me |
| vk.me |
| ig.me |
| www.tiktok.com |
| Subject Issuer | Validity | Valid | |
|---|---|---|---|
| radiobalkanfox.com WE1 |
2026-09-02 - 2026-12-01 |
3mo | crt.sh |
| upload.video.google.com WE2 |
2026-09-18 - 2026-12-11 |
3mo | crt.sh |
| *.google-analytics.com WE2 |
2026-09-18 - 2026-12-11 |
3mo | crt.sh |
| gravatar.com YE1 |
2026-10-07 - 2027-01-05 |
3mo | crt.sh |
| *.facebook.com DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2026-07-17 - 2026-10-15 |
3mo | crt.sh |
| cloudflareinsights.com WE1 |
2026-08-14 - 2026-11-12 |
3mo | crt.sh |
| buttonizer.io WE1 |
2026-09-19 - 2026-12-18 |
3mo | crt.sh |
| *.gstatic.com WE2 |
2026-09-18 - 2026-12-11 |
3mo | crt.sh |
| *.24sata.hr Go Daddy Secure Certificate Authority - G2 |
2026-02-10 - 2027-02-25 |
1yr | crt.sh |
| *.google.com WR2 |
2026-09-10 - 2026-12-03 |
3mo | crt.sh |
| *.doubleclick.net WE2 |
2026-09-18 - 2026-12-11 |
3mo | crt.sh |
| *.ftlv21-1.fna.fbcdn.net DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2026-08-27 - 2026-11-25 |
3mo | crt.sh |
| edgestatic.com WR2 |
2026-09-18 - 2026-12-11 |
3mo | crt.sh |
This page contains 4 frames:
Primary Page:
https://www.radiobalkanfox.com/bivsi-agent-meghan-markle-odlicno-je-sto-ne-radim-s-njom/
Frame ID: 0C27334B28569AAF462487709E236ED6
Requests: 92 HTTP requests in this frame
Frame:
https://www.facebook.com/v25.0/plugins/page.php?adapt_container_width=false&app_id=&channel=https%3A%2F%2Fstaticxx.facebook.com%2Fx%2Fconnect%2Fxd_arbiter%2F%3Fversion%3D46%23cb%3Dfbd6267469cc8199a%26domain%3Dwww.radiobalkanfox.com%26is_canvas%3Dfalse%26origin%3Dhttps%253A%252F%252Fwww.radiobalkanfox.com%252Ff66d045fde45fea23%26relation%3Dparent.parent&container_width=0&height=500&hide_cover=false&href=https%3A%2F%2Fwww.facebook.com%2Fradiobalkanfox&lazy=false&locale=en_US&sdk=joey&show_facepile=false&small_header=false&tabs=timeline&width=300
Frame ID: 373D28910684A345515E4BD2ECFA6C0C
Requests: 28 HTTP requests in this frame
Frame:
https://www.youtube.com/embed/bkQhF2ZZ2Sg?controls=0&rel=0&disablekb=1&showinfo=0&modestbranding=0&html5=1&iv_load_policy=3&autoplay=0&end=0&loop=0&playsinline=0&start=0&nocookie=false&enablejsapi=1&origin=https%3A%2F%2Fwww.radiobalkanfox.com&widgetid=1&forigin=https%3A%2F%2Fwww.radiobalkanfox.com%2Fbivsi-agent-meghan-markle-odlicno-je-sto-ne-radim-s-njom%2F&aoriginsup=1&vf=1
Frame ID: E4BF6CC4512363F9071FDCC8924C85F0
Requests: 14 HTTP requests in this frame
Frame:
https://www.facebook.com/v25.0/plugins/page.php?adapt_container_width=false&app_id=&channel=https%3A%2F%2Fstaticxx.facebook.com%2Fx%2Fconnect%2Fxd_arbiter%2F%3Fversion%3D46%23cb%3Df1f50819c6babaf0d%26domain%3Dwww.radiobalkanfox.com%26is_canvas%3Dfalse%26origin%3Dhttps%253A%252F%252Fwww.radiobalkanfox.com%252Ff66d045fde45fea23%26relation%3Dparent.parent&container_width=300&height=500&hide_cover=false&href=https%3A%2F%2Fwww.facebook.com%2Fradiobalkanfox&lazy=false&locale=en_US&sdk=joey&show_facepile=false&small_header=false&tabs=timeline&width=300
Frame ID: 8124E9D0EF2145A367769679D4878112
Requests: 27 HTTP requests in this frame
Screenshot
Go Pro
Only in urlscan Pro
Use the Visual Search feature to find pages with visually similar screenshots.
Click for more information
Free trials of urlscan Pro are available.
Page Title
Bivši agent Meghan Markle: ‘Odlično je što ne radim s njom’ – Radio BalkanFoxDetected technologies
 WordPress
(CMS)
Expand
Detected patterns
- /wp-(?:content|includes)/
 YouTube
(Video players)
Expand
Detected patterns
- \.youtube\.com/
 Buttonizer
(Widgets)
Expand
Detected patterns
- cdn\.buttonizer\.io/
 Cloudflare Browser Insights
(Analytics)
Expand
Detected patterns
- static\.cloudflareinsights\.com/beacon(?:\.min)?\.js
 DoubleClick Floodlight
(Advertising)
Expand
Detected patterns
- \.doubleclick\.net
 Facebook Pixel
(Analytics)
Expand
Detected patterns
- connect\.facebook\.\w+/.+/fbevents\.js
- connect\.facebook.\w+/signals/config/\d+\?v=([\d\.]+)
 Font Awesome
(Font scripts)
Expand
Detected patterns
- (?:F|f)o(?:n|r)t-?(?:A|a)wesome(?:.*?([0-9a-fA-F]{7,40}|[\d]+(?:.[\d]+(?:.[\d]+)?)?)|)
 Google Analytics
(Analytics)
Expand
Detected patterns
- googletagmanager\.com/gtag/js
- google-analytics\.com/(?:ga|urchin|analytics)\.js
 Google Tag Manager
(Tag managers)
Expand
Detected patterns
- \.googletagmanager\.com/
imagesLoaded (JavaScript libraries) Expand
Detected patterns
- imagesloaded(?:\.min)?\.js(?:\?v(?:er)?=((?:\d+\.)+\d+))?
 jQuery
(JavaScript libraries)
Expand
Detected patterns
- jquery
jQuery Migrate
(JavaScript libraries)
Expand
Detected patterns
- jquery-migrate(?:\.min)?(?:-)?(?:\.min)?\.js(?:\?v(?:er)?=((?:\d+\.)+\d+))?
- jquery-migrate(?:\.min)?(?:-?((?:\d+\.)+\d+))?(?:\.min)?\.js
 Mailcheck
(JavaScript libraries)
Expand
Detected patterns
- mailcheck(?:\.min)?\.js(?:\?v(?:er)?=(\d+\.\d+\.\d+))?
 Underscore.js
(JavaScript libraries)
Expand
Detected patterns
- underscore.*\.js(?:\?ver=([\d.]+))?
Page Statistics
12 Outgoing links
Go Pro
Only in urlscan Pro
Effortlessly use any on-page link as a pivot to discover other pages pointing to the exact same destination. Seamlessly trace both specific URLs and broader domains to uncover hidden connection networks and map out backlink relationships with ease.
Click for more information
Free trials of urlscan Pro are available.
These are links going to different origins than the main page.
Title: Balkanfox Club
Search URL Search Domain Scan URL
Title: Radio serveri
Search URL Search Domain Scan URL
Title: WhatsApp
Search URL Search Domain Scan URL
Title: Meghan Markle
Search URL Search Domain Scan URL
Title: Sunday Times
Search URL Search Domain Scan URL
Title: Page Six
Search URL Search Domain Scan URL
Title: 24sata
Search URL Search Domain Scan URL
Title: https://www.youtube.com/watch?v=bkQhF2ZZ2Sg
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Redirected requests
There were HTTP redirect chains for the following requests:
Request Chain 112- https://googleads.g.doubleclick.net/pagead/id HTTP 302
- https://googleads.g.doubleclick.net/pagead/id?slf_rd=1
163 HTTP transactions
Go Pro
Only in urlscan Pro
Inspect WebSocket connections, examine POST data effortlessly, and track overlap counts in real time. Features live search and filtering across all HTTP output, complete with full response metadata for deep analysis.
Click for more information
Free trials of urlscan Pro are available.
0 data transactions
| Method Protocol |
Status | Resource Path |
Size x-fer |
Time Latency |
Type MIME-Type |
IP Location |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
|
GET H2 |
200 |
Primary Request
/
Show response
www.radiobalkanfox.com/bivsi-agent-meghan-markle-odlicno-je-sto-ne-radim-s-njom/ |
120 KB 33 KB |
463ms
326ms |
Document
text/html |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
images-2021-33-pxl-pa-031018-22208073-1200x500.jpg
www.radiobalkanfox.com/wp-content/uploads/2026/09/ |
32 KB 32 KB |
253ms
251ms |
Image
image/jpeg |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
wpp.min.js
Show response
www.radiobalkanfox.com/wp-content/plugins/wordpress-popular-posts/assets/js/ |
4 KB 2 KB |
243ms
241ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
style.css
www.radiobalkanfox.com/wp-content/plugins/facebook-pagelike-widget/assets/css/ |
711 B 723 B |
230ms
228ms |
Stylesheet
text/css |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
wpa.css
www.radiobalkanfox.com/wp-content/plugins/honeypot/includes/css/ |
759 B 714 B |
254ms
252ms |
Stylesheet
text/css |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
wp-automatic.css
www.radiobalkanfox.com/wp-content/plugins/wp-automatic/css/ |
3 KB 1000 B |
249ms
247ms |
Stylesheet
text/css |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
wpp.css
www.radiobalkanfox.com/wp-content/plugins/wordpress-popular-posts/assets/css/ |
2 KB 943 B |
239ms
237ms |
Stylesheet
text/css |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
css
fonts.googleapis.com/ |
4 KB 1 KB |
369ms
127ms |
Stylesheet
text/css |
142.251.13.95 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
min.css
www.radiobalkanfox.com/wp-content/themes/gridlove/assets/css/ |
194 KB 37 KB |
256ms
255ms |
Stylesheet
text/css |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
style.css
www.radiobalkanfox.com/wp-content/plugins/chaty/dist/css/ |
36 KB 8 KB |
274ms
268ms |
Stylesheet
text/css |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
main.css
www.radiobalkanfox.com/wp-content/plugins/meks-easy-social-share/assets/css/ |
9 KB 2 KB |
275ms
269ms |
Stylesheet
text/css |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
jquery.min.js
Show response
www.radiobalkanfox.com/wp-includes/js/jquery/ |
86 KB 32 KB |
277ms
271ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
jquery-migrate.min.js
Show response
www.radiobalkanfox.com/wp-includes/js/jquery/ |
13 KB 5 KB |
277ms
272ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
main-front.js
Show response
www.radiobalkanfox.com/wp-content/plugins/wp-automatic/js/ |
2 KB 901 B |
276ms
271ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
js
Show response
www.googletagmanager.com/gtag/ |
341 KB 122 KB |
389ms
143ms |
Script
application/javascript |
142.251.20.97 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
mediaelementplayer-legacy.min.css
www.radiobalkanfox.com/wp-includes/js/mediaelement/ |
11 KB 3 KB |
274ms
269ms |
Stylesheet
text/css |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
wp-mediaelement.min.css
www.radiobalkanfox.com/wp-includes/js/mediaelement/ |
4 KB 2 KB |
277ms
272ms |
Stylesheet
text/css |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
frontend.css
www.radiobalkanfox.com/wp-content/plugins/radio-player-premium/assets/css/ |
60 KB 10 KB |
279ms
274ms |
Stylesheet
text/css |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
500 |
logo-3.png
www.radiobalkanfox.com/wp-content/uploads/2026/01/ |
588 B 588 B |
485ms
480ms |
Image
text/html |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
22166bf34502ba2fc2d271d1848215034ba5e3e36340297535107a924daa9e68
secure.gravatar.com/avatar/ |
2 KB 2 KB |
357ms
117ms |
Image
image/png |
192.0.73.2 Automattic |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
email-decode.min.js
Show response
www.radiobalkanfox.com/cdn-cgi/scripts/5c5dd728/cloudflare-static/ |
1 KB 1 KB |
67ms
65ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
sdk.js
Show response
connect.facebook.net/en_US/ |
12 KB 5 KB |
233ms
114ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
22166bf34502ba2fc2d271d1848215034ba5e3e36340297535107a924daa9e68
secure.gravatar.com/avatar/ |
16 KB 16 KB |
360ms
119ms |
Image
image/png |
192.0.73.2 Automattic |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
asyncjs.php
ads.qaquicky.com/www/delivery/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
loader.gif
www.radiobalkanfox.com/wp-content/plugins/facebook-pagelike-widget/assets/images/ |
8 KB 8 KB |
184ms
182ms |
Image
image/gif |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
wpa.js
Show response
www.radiobalkanfox.com/wp-content/plugins/honeypot/includes/js/ |
6 KB 2 KB |
120ms
120ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
comment-reply.min.js
Show response
www.radiobalkanfox.com/wp-includes/js/ |
3 KB 2 KB |
199ms
197ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
imagesloaded.min.js
Show response
www.radiobalkanfox.com/wp-includes/js/ |
5 KB 2 KB |
244ms
244ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
masonry.min.js
Show response
www.radiobalkanfox.com/wp-includes/js/ |
24 KB 8 KB |
247ms
242ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
jquery.masonry.min.js
Show response
www.radiobalkanfox.com/wp-includes/js/jquery/ |
2 KB 1 KB |
133ms
127ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
min.js
Show response
www.radiobalkanfox.com/wp-content/themes/gridlove/assets/js/ |
87 KB 26 KB |
194ms
189ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
script.js
Show response
www.radiobalkanfox.com/wp-content/plugins/chaty/dist/js/ |
100 KB 28 KB |
253ms
251ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
mailcheck.js
Show response
www.radiobalkanfox.com/wp-content/plugins/chaty/admin/assets/js/ |
7 KB 3 KB |
198ms
197ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
picmo-umd.min.js
Show response
www.radiobalkanfox.com/wp-content/plugins/chaty/admin/assets/js/ |
92 KB 27 KB |
184ms
179ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
picmo-latest-umd.min.js
Show response
www.radiobalkanfox.com/wp-content/plugins/chaty/admin/assets/js/ |
19 KB 8 KB |
191ms
186ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
main.js
Show response
www.radiobalkanfox.com/wp-content/plugins/meks-easy-social-share/assets/js/ |
551 B 641 B |
133ms
128ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
akismet-frontend.js
Show response
www.radiobalkanfox.com/wp-content/plugins/akismet/_inc/ |
12 KB 4 KB |
258ms
257ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
mediaelement-and-player.min.js
Show response
www.radiobalkanfox.com/wp-includes/js/mediaelement/ |
154 KB 40 KB |
198ms
193ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
mediaelement-migrate.min.js
Show response
www.radiobalkanfox.com/wp-includes/js/mediaelement/ |
1 KB 923 B |
131ms
126ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
wp-mediaelement.min.js
Show response
www.radiobalkanfox.com/wp-includes/js/mediaelement/ |
1 KB 824 B |
134ms
129ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
vimeo.min.js
Show response
www.radiobalkanfox.com/wp-includes/js/mediaelement/renderers/ |
6 KB 3 KB |
133ms
129ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
fb.js
Show response
www.radiobalkanfox.com/wp-content/plugins/facebook-pagelike-widget/assets/js/ |
2 KB 960 B |
131ms
126ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
sdk.js
Show response
connect.facebook.net/sr_RS/ |
12 KB 5 KB |
367ms
237ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
react.min.js
Show response
www.radiobalkanfox.com/wp-includes/js/dist/vendor/ |
10 KB 5 KB |
330ms
326ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
react-dom.min.js
Show response
www.radiobalkanfox.com/wp-includes/js/dist/vendor/ |
129 KB 44 KB |
239ms
235ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
escape-html.min.js
Show response
www.radiobalkanfox.com/wp-includes/js/dist/ |
1 KB 934 B |
255ms
251ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
element.min.js
Show response
www.radiobalkanfox.com/wp-includes/js/dist/ |
12 KB 6 KB |
134ms
131ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
underscore.min.js
Show response
www.radiobalkanfox.com/wp-includes/js/ |
19 KB 8 KB |
136ms
133ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
wp-util.min.js
Show response
www.radiobalkanfox.com/wp-includes/js/ |
1 KB 1 KB |
270ms
266ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
hooks.min.js
Show response
www.radiobalkanfox.com/wp-includes/js/dist/ |
5 KB 2 KB |
188ms
185ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
i18n.min.js
Show response
www.radiobalkanfox.com/wp-includes/js/dist/ |
6 KB 3 KB |
130ms
126ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
react-player.min.js
Show response
www.radiobalkanfox.com/wp-content/plugins/radio-player-premium/assets/vendor/ |
56 KB 17 KB |
199ms
195ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
frontend.js
Show response
www.radiobalkanfox.com/wp-content/plugins/radio-player-premium/assets/js/ |
88 KB 28 KB |
326ms
323ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
v4bc70e2c01a94c73b74392e4234840661791215815920
Show response
static.cloudflareinsights.com/beacon.min.js/ |
31 KB 10 KB |
203ms
74ms |
Script
text/javascript |
104.16.80.73 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
201 |
1272519
Show response
www.radiobalkanfox.com/wp-json/wordpress-popular-posts/v2/views/ |
54 B 714 B |
331ms
330ms |
Fetch
application/json |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
fbevents.js
Show response
connect.facebook.net/en_US/ |
419 KB 110 KB |
251ms
124ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
embed.js
Show response
cdn.buttonizer.io/ |
641 B 771 B |
210ms
73ms |
Script
application/javascript |
172.67.71.68 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
u-4i0qWljRw-PfU81xCKCpdpbgZJl6Xvqdns.woff2
fonts.gstatic.com/s/cabin/v35/ |
28 KB 28 KB |
378ms
252ms |
Font
font/woff2 |
192.178.183.94 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
fontawesome-webfont.woff2
www.radiobalkanfox.com/wp-content/themes/gridlove/assets/fonts/ |
80 KB 80 KB |
271ms
270ms |
Font
font/woff2 |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
socicon.woff
www.radiobalkanfox.com/wp-content/plugins/meks-easy-social-share/assets/fonts/ |
98 KB 98 KB |
294ms
293ms |
Font
font/woff |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
S6u9w4BMUTPHh6UVSwiPGQ.woff2
fonts.gstatic.com/s/lato/v25/ |
23 KB 23 KB |
333ms
208ms |
Font
font/woff2 |
192.178.183.94 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
u-4i0qWljRw-PfU81xCKCpdpbgZJl6Xvp9nsBXw.woff2
fonts.gstatic.com/s/cabin/v35/ |
16 KB 16 KB |
246ms
121ms |
Font
font/woff2 |
192.178.183.94 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
S6u9w4BMUTPHh6UVSwaPGR_p.woff2
fonts.gstatic.com/s/lato/v25/ |
5 KB 5 KB |
321ms
196ms |
Font
font/woff2 |
192.178.183.94 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
S6uyw4BMUTPHjx4wXg.woff2
fonts.gstatic.com/s/lato/v25/ |
23 KB 23 KB |
277ms
152ms |
Font
font/woff2 |
192.178.183.94 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
profimedia-0856925887.jpg
img.24sata.hr/WPhp8EODM0P8Ew-2xdgd2wCJx6Q=/0x0:1390x839/622x0/media/images/2024-16/ |
13 KB 13 KB |
498ms
183ms |
Image
image/webp |
91.207.22.61 SATA-AS 24sata doo |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
images-2023-37-pxl-nisynd-130923-103158049.jpg
img.24sata.hr/G5YJC4eABLW0wilMl8SmqyfGI5s=/622x0/smart/media/images/2023-39/ |
14 KB 14 KB |
579ms
264ms |
Image
image/webp |
91.207.22.61 SATA-AS 24sata doo |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
ml-1-385x300.jpg
www.radiobalkanfox.com/wp-content/uploads/2026/10/ |
23 KB 24 KB |
241ms
240ms |
Image
image/jpeg |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
najnovija-vest-telegraf.rs-1200x630-385x300.webp
www.radiobalkanfox.com/wp-content/uploads/2026/08/ |
12 KB 12 KB |
214ms
213ms |
Image
image/webp |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
Husein-Alijevic-Husa-Dr-Igi-dr-Iggy-385x300.jpg
www.radiobalkanfox.com/wp-content/uploads/2026/10/ |
19 KB 19 KB |
345ms
343ms |
Image
image/jpeg |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
embed.js
Show response
cdn.buttonizer.io/static/build-v4.15.4/assets/ |
42 B 511 B |
292ms
158ms |
Script
application/javascript |
172.67.71.68 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
/
Show response
connect.facebook.net/en_US/bundle/sdk.js/ |
263 KB 78 KB |
116ms
116ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
radiobalkanfox.png
www.radiobalkanfox.com/wp-content/uploads/2026/09/ |
34 KB 34 KB |
184ms
184ms |
Image
image/png |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
admin-ajax.php
Show response
www.radiobalkanfox.com/wp-admin/ |
234 B 493 B |
693ms
692ms |
XHR
application/json |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
51e896c7-3dc4-48f1-a588-1d0487c6e338
https://www.radiobalkanfox.com/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
admin-ajax.php
Show response
www.radiobalkanfox.com/wp-admin/ |
1 B 564 B |
451ms
450ms |
XHR
text/html |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
player_api
Show response
www.youtube.com/ |
993 B 4 KB |
342ms
149ms |
Script
text/javascript |
142.251.151.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
mejs-controls.svg
www.radiobalkanfox.com/wp-includes/js/mediaelement/ |
4 KB 2 KB |
254ms
254ms |
Image
image/svg+xml |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
500 |
whatsapp.png
www.radiobalkanfox.com/images/ |
588 B 588 B |
337ms
337ms |
Image
text/html |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
500 |
logo-3.png
www.radiobalkanfox.com/wp-content/uploads/2026/01/ |
588 B 588 B |
370ms
370ms |
Image
text/html |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
watch
www.youtube.com/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
wp-emoji-release.min.js
Show response
www.radiobalkanfox.com/wp-includes/js/ |
22 KB 6 KB |
126ms
125ms |
Script
application/javascript |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
page.php
Show response
www.facebook.com/v25.0/plugins/ Frame 373D |
84 KB 22 KB |
355ms
237ms |
Document
text/html |
57.144.244.1 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
buttonizer_DvrWDH.js
Show response
cdn.buttonizer.io/static/build-v4.15.4/assets/js/widget/ |
381 KB 125 KB |
226ms
226ms |
Script
application/javascript |
172.67.71.68 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
877514510584268
Show response
connect.facebook.net/signals/config/ |
395 KB 99 KB |
229ms
223ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
js
Show response
www.googletagmanager.com/gtag/ |
485 KB 164 KB |
140ms
139ms |
Script
application/javascript |
142.251.20.97 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
analytics.js
Show response
www.google-analytics.com/ |
51 KB 21 KB |
359ms
117ms |
Script
text/javascript |
142.251.14.139 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
www-widgetapi.js
Show response
www.youtube.com/s/player/f2999a12/www-widgetapi.vflset/ |
26 KB 9 KB |
146ms
145ms |
Script
text/javascript |
142.251.151.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
/
www.facebook.com/tr/ |
0 20 B |
241ms
120ms |
Image
text/plain |
57.144.244.1 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
u-3S4qCLYzN.css
static.xx.fbcdn.net/rsrc.php/v5/yJ/l/0,cross/ Frame 373D |
17 KB 5 KB |
270ms
133ms |
Stylesheet
text/css |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
C4ui2BVlFmW.css
static.xx.fbcdn.net/rsrc.php/v5/yd/l/0,cross/ Frame 373D |
2 KB 612 B |
269ms
133ms |
Stylesheet
text/css |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
ZnA3Zd6g5rR.css
static.xx.fbcdn.net/rsrc.php/v5/yl/l/0,cross/ Frame 373D |
1 MB 225 KB |
270ms
134ms |
Stylesheet
text/css |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
hBabt8AJOVM.css
static.xx.fbcdn.net/rsrc.php/v5/yJ/l/0,cross/ Frame 373D |
365 KB 46 KB |
269ms
133ms |
Stylesheet
text/css |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
qLRgpgOaLjE.css
static.xx.fbcdn.net/rsrc.php/v5/yH/l/0,cross/ Frame 373D |
10 KB 4 KB |
270ms
134ms |
Stylesheet
text/css |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
z2Jw0N6tzXZ.js
Show response
static.xx.fbcdn.net/rsrc.php/v4/yr/r/ Frame 373D |
378 KB 99 KB |
645ms
509ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
XghMO1E1Jid.js
Show response
static.xx.fbcdn.net/rsrc.php/v4/yk/r/ Frame 373D |
20 KB 7 KB |
674ms
537ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
a1Hjgn3y0c_.js
Show response
static.xx.fbcdn.net/rsrc.php/v4issO4/yz/l/en_US-j/ Frame 373D |
73 KB 22 KB |
675ms
539ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
dB_hPuUuBYU.js
Show response
static.xx.fbcdn.net/rsrc.php/v4i7M54/yn/l/en_US-j/ Frame 373D |
70 KB 21 KB |
679ms
543ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
PlaVMt6INY_.js
Show response
static.xx.fbcdn.net/rsrc.php/v4/yC/r/ Frame 373D |
42 KB 14 KB |
716ms
580ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
e0qnL2dG90H.js
Show response
static.xx.fbcdn.net/rsrc.php/v4/yt/r/ Frame 373D |
2 KB 1 KB |
717ms
581ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
OAwQqXTqHXQ.js
Show response
static.xx.fbcdn.net/rsrc.php/v4iLl54/ye/l/en_US-j/ Frame 373D |
86 KB 19 KB |
719ms
583ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
gOghsSLR_T5.js
Show response
static.xx.fbcdn.net/rsrc.php/v4iLpP4/yk/l/en_US-j/ Frame 373D |
160 KB 43 KB |
741ms
605ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
4m_Xra5XEpc.js
Show response
static.xx.fbcdn.net/rsrc.php/v4iHj84/yI/l/en_US-j/ Frame 373D |
104 KB 28 KB |
754ms
618ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
wtuZmcjZpl1.js
Show response
static.xx.fbcdn.net/rsrc.php/v4ijeu4/yt/l/en_US-j/ Frame 373D |
391 KB 100 KB |
756ms
619ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
_5O1nAFpa3p.js
Show response
static.xx.fbcdn.net/rsrc.php/v4/yA/r/ Frame 373D |
8 KB 3 KB |
771ms
635ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
collect
www.google-analytics.com/g/ |
0 0 |
125ms
125ms |
Fetch
text/plain |
142.251.14.139 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
embed.css
Show response
cdn.buttonizer.io/static/build-v4.15.4/assets/ |
39 KB 7 KB |
147ms
146ms |
XHR
text/css |
172.67.71.68 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
404 |
101e53ab-912c-4c30-bf7a-107ec9930d47
Show response
api.buttonizer.io/serve/ |
68 B 356 B |
173ms
172ms |
XHR
text/plain |
172.67.71.68 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
OPTIONS H2 |
200 |
101e53ab-912c-4c30-bf7a-107ec9930d47
api.buttonizer.io/serve/ Frame |
0 0 |
88ms
79ms |
Preflight
text/plain |
172.67.71.68 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
bkQhF2ZZ2Sg
Show response
www.youtube.com/embed/ Frame E4BF |
156 KB 64 KB |
375ms
191ms |
Document
text/html |
142.251.153.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
www-player-rtl.css
www.youtube.com/s/player/f2999a12/ Frame E4BF |
539 KB 58 KB |
123ms
122ms |
Stylesheet
text/css |
142.251.153.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
m=root,base
www.youtube.com/s/_/ytembeds/_/ss/k=ytembeds.base.pjfgqZWK4F4.R.W.O/am=AAAAQADG/d=1/br=1/rs=AGKMywF4RxGeBmGtYRnIMAEafuHhaoVs6w/ Frame E4BF |
11 KB 3 KB |
179ms
179ms |
Stylesheet
text/css |
142.251.153.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
m=root,base
Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.KnLLmnw14PA.2021.O/am=AAAAQADG/d=1/excm=base,root/br=1/rs=AGKMywGA7wrLiSC6AmQ1fWLJ64CF29Sgew/ Frame E4BF |
473 KB 160 KB |
165ms
165ms |
Script
text/javascript |
142.251.153.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
base.js
Show response
www.youtube.com/s/player/f2999a12/player_embed_es6.vflset/iw_IL/ Frame E4BF |
2 MB 473 KB |
106ms
106ms |
Script
text/javascript |
142.251.153.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
id
Show response
googleads.g.doubleclick.net/pagead/ Frame E4BF Redirect Chain
|
100 B 146 B |
127ms
127ms |
XHR
application/json |
142.250.154.155 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
ad_status.js
Show response
static.doubleclick.net/instream/ Frame E4BF |
29 B 495 B |
365ms
117ms |
Script
text/javascript |
142.251.13.148 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
m=r78Drb
Show response
www.youtube.com/s/_/ytembeds/_/js/k=ytembeds.base.en_US.KnLLmnw14PA.2021.O/ck=ytembeds.base.pjfgqZWK4F4.R.W.O/am=AAAAQADG/d=1/exm=base,root/excm=base,root/ed=1/br=1/rs=AGKMywFoJCPccQHm_Z6oMUQ9n-2td... Frame E4BF |
919 KB 221 KB |
65ms
65ms |
Script
text/javascript |
142.251.153.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
yEEx7Mog7nhOLFp0H8UYN6F4MpFZ67ZiE2zcSXpWIUQ.js
Show response
www.google.com/js/th/ Frame E4BF |
62 KB 24 KB |
191ms
66ms |
Script
text/javascript |
142.251.155.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
FsZfqyRF5_K.js
Show response
static.xx.fbcdn.net/rsrc.php/v4/yt/r/ Frame 373D |
32 KB 11 KB |
124ms
124ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
LIe5AObKQl0.js
Show response
static.xx.fbcdn.net/rsrc.php/v4/yx/r/ Frame 373D |
243 KB 68 KB |
122ms
122ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
404 |
/
Show response
www.facebook.com/platform/plugin/page/logging/ Frame 373D |
72 B 192 B |
139ms
139ms |
XHR
text/html |
57.144.244.1 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
511148448_1336221345177888_6068519041685972968_n.jpg
scontent.ftlv21-1.fna.fbcdn.net/v/t39.30808-1/ Frame 373D |
4 KB 4 KB |
284ms
215ms |
Image
image/jpeg |
45.80.89.83 Exelera-AS Exeler... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
540679465_1402643438535678_3731021812369427450_n.jpg
scontent.ftlv21-1.fna.fbcdn.net/v/t39.30808-6/ Frame 373D |
14 KB 14 KB |
221ms
152ms |
Image
image/jpeg |
45.80.89.83 Exelera-AS Exeler... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
8894512731562856904
external.ftlv21-1.fna.fbcdn.net/emg1/v/t13/ Frame 373D |
6 KB 6 KB |
356ms
272ms |
Image
image/jpeg |
45.80.89.83 Exelera-AS Exeler... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
3440068044086736716
external.ftlv21-1.fna.fbcdn.net/emg1/v/t13/ Frame 373D |
12 KB 12 KB |
223ms
140ms |
Image
image/jpeg |
45.80.89.83 Exelera-AS Exeler... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
1399675481977049450
external.ftlv21-1.fna.fbcdn.net/emg1/v/t13/ Frame 373D |
10 KB 10 KB |
284ms
201ms |
Image
image/jpeg |
45.80.89.83 Exelera-AS Exeler... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
17966172995204065269
external.ftlv21-1.fna.fbcdn.net/emg1/v/t13/ Frame 373D |
6 KB 6 KB |
252ms
169ms |
Image
image/jpeg |
45.80.89.83 Exelera-AS Exeler... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
7468624982115508596
external.ftlv21-1.fna.fbcdn.net/emg1/v/t13/ Frame 373D |
9 KB 9 KB |
356ms
273ms |
Image
image/jpeg |
45.80.89.83 Exelera-AS Exeler... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
KFO7CnqEu92Fr1ME7kSn66aGLdTylUAMa3yUBA.woff2
fonts.gstatic.com/s/roboto/v48/ Frame E4BF |
39 KB 39 KB |
242ms
117ms |
Font
font/woff2 |
192.178.183.94 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
default.webp
i.ytimg.com/vi_webp/bkQhF2ZZ2Sg/ Frame E4BF |
1 KB 2 KB |
385ms
135ms |
Image
image/webp |
142.250.154.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
204 |
generate_204
www.youtube.com/ Frame E4BF |
0 10 B |
66ms
65ms |
Image
text/plain |
142.251.155.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
200 |
GenerateIT
Show response
jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/ Frame E4BF |
98 B 308 B |
132ms
131ms |
XHR
application/json+protobuf |
172.217.116.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
OPTIONS H2 |
200 |
GenerateIT
jnn-pa.googleapis.com/$rpc/google.internal.waa.v1.Waa/ Frame |
0 0 |
310ms
124ms |
Preflight
text/html |
172.217.116.4 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST |
|
bz
www.facebook.com/ajax/ Frame 373D |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
page.php
Show response
www.facebook.com/v25.0/plugins/ Frame 8124 |
84 KB 22 KB |
258ms
258ms |
Document
text/html |
57.144.244.1 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H2 |
204 |
rum
Show response
www.radiobalkanfox.com/cdn-cgi/ |
0 401 B |
66ms
65ms |
XHR
text/plain |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
u-3S4qCLYzN.css
static.xx.fbcdn.net/rsrc.php/v5/yJ/l/0,cross/ Frame 8124 |
17 KB 0 |
0ms
0ms |
Stylesheet
text/css |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
C4ui2BVlFmW.css
static.xx.fbcdn.net/rsrc.php/v5/yd/l/0,cross/ Frame 8124 |
2 KB 0 |
1ms
1ms |
Stylesheet
text/css |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
y8yjB9DNoI5.css
static.xx.fbcdn.net/rsrc.php/v5/yX/l/0,cross/ Frame 8124 |
1 MB 225 KB |
122ms
122ms |
Stylesheet
text/css |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
hBabt8AJOVM.css
static.xx.fbcdn.net/rsrc.php/v5/yJ/l/0,cross/ Frame 8124 |
365 KB 0 |
269ms
133ms |
Stylesheet
text/css |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
qLRgpgOaLjE.css
static.xx.fbcdn.net/rsrc.php/v5/yH/l/0,cross/ Frame 8124 |
10 KB 0 |
1ms
1ms |
Stylesheet
text/css |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
z2Jw0N6tzXZ.js
Show response
static.xx.fbcdn.net/rsrc.php/v4/yr/r/ Frame 8124 |
378 KB 0 |
645ms
509ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
XghMO1E1Jid.js
Show response
static.xx.fbcdn.net/rsrc.php/v4/yk/r/ Frame 8124 |
20 KB 0 |
674ms
537ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
a1Hjgn3y0c_.js
Show response
static.xx.fbcdn.net/rsrc.php/v4issO4/yz/l/en_US-j/ Frame 8124 |
73 KB 0 |
675ms
539ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
dB_hPuUuBYU.js
Show response
static.xx.fbcdn.net/rsrc.php/v4i7M54/yn/l/en_US-j/ Frame 8124 |
70 KB 0 |
679ms
543ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
PlaVMt6INY_.js
Show response
static.xx.fbcdn.net/rsrc.php/v4/yC/r/ Frame 8124 |
42 KB 0 |
716ms
580ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
e0qnL2dG90H.js
Show response
static.xx.fbcdn.net/rsrc.php/v4/yt/r/ Frame 8124 |
2 KB 0 |
717ms
581ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
OAwQqXTqHXQ.js
Show response
static.xx.fbcdn.net/rsrc.php/v4iLl54/ye/l/en_US-j/ Frame 8124 |
86 KB 0 |
719ms
583ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
gOghsSLR_T5.js
Show response
static.xx.fbcdn.net/rsrc.php/v4iLpP4/yk/l/en_US-j/ Frame 8124 |
160 KB 0 |
741ms
605ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
4m_Xra5XEpc.js
Show response
static.xx.fbcdn.net/rsrc.php/v4iHj84/yI/l/en_US-j/ Frame 8124 |
104 KB 0 |
754ms
618ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
_uI8PC9hP6s.js
Show response
static.xx.fbcdn.net/rsrc.php/v4ijeu4/yK/l/en_US-j/ Frame 8124 |
391 KB 100 KB |
138ms
138ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
_5O1nAFpa3p.js
Show response
static.xx.fbcdn.net/rsrc.php/v4/yA/r/ Frame 8124 |
8 KB 0 |
771ms
635ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
FsZfqyRF5_K.js
Show response
static.xx.fbcdn.net/rsrc.php/v4/yt/r/ Frame 8124 |
32 KB 0 |
124ms
124ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
EPsZWxuz3pJ.js
Show response
static.xx.fbcdn.net/rsrc.php/v4/yQ/r/ Frame 8124 |
243 KB 68 KB |
122ms
122ms |
Script
application/x-javascript |
157.240.0.6 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
404 |
/
Show response
www.facebook.com/platform/plugin/page/logging/ Frame 8124 |
72 B 192 B |
142ms
141ms |
XHR
text/html |
57.144.244.1 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
511148448_1336221345177888_6068519041685972968_n.jpg
scontent.ftlv21-1.fna.fbcdn.net/v/t39.30808-1/ Frame 8124 |
4 KB 0 |
0ms
0ms |
Image
image/jpeg |
45.80.89.83 Exelera-AS Exeler... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
540679465_1402643438535678_3731021812369427450_n.jpg
scontent.ftlv21-1.fna.fbcdn.net/v/t39.30808-6/ Frame 8124 |
14 KB 0 |
1ms
1ms |
Image
image/jpeg |
45.80.89.83 Exelera-AS Exeler... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
8894512731562856904
external.ftlv21-1.fna.fbcdn.net/emg1/v/t13/ Frame 8124 |
6 KB 0 |
1ms
1ms |
Image
image/jpeg |
45.80.89.83 Exelera-AS Exeler... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
3440068044086736716
external.ftlv21-1.fna.fbcdn.net/emg1/v/t13/ Frame 8124 |
12 KB 0 |
1ms
1ms |
Image
image/jpeg |
45.80.89.83 Exelera-AS Exeler... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
1399675481977049450
external.ftlv21-1.fna.fbcdn.net/emg1/v/t13/ Frame 8124 |
10 KB 0 |
1ms
1ms |
Image
image/jpeg |
45.80.89.83 Exelera-AS Exeler... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
17966172995204065269
external.ftlv21-1.fna.fbcdn.net/emg1/v/t13/ Frame 8124 |
6 KB 0 |
1ms
1ms |
Image
image/jpeg |
45.80.89.83 Exelera-AS Exeler... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
7468624982115508596
external.ftlv21-1.fna.fbcdn.net/emg1/v/t13/ Frame 8124 |
9 KB 0 |
1ms
1ms |
Image
image/jpeg |
45.80.89.83 Exelera-AS Exeler... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
cropped-faviconrbf-32x32.png
www.radiobalkanfox.com/wp-content/uploads/2026/08/ |
2 KB 3 KB |
126ms
126ms |
Other
image/png |
172.67.146.243 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
200 |
log_event
Show response
www.youtube.com/youtubei/v1/ Frame E4BF |
28 B 50 B |
130ms
127ms |
XHR
application/json |
142.251.155.119 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||


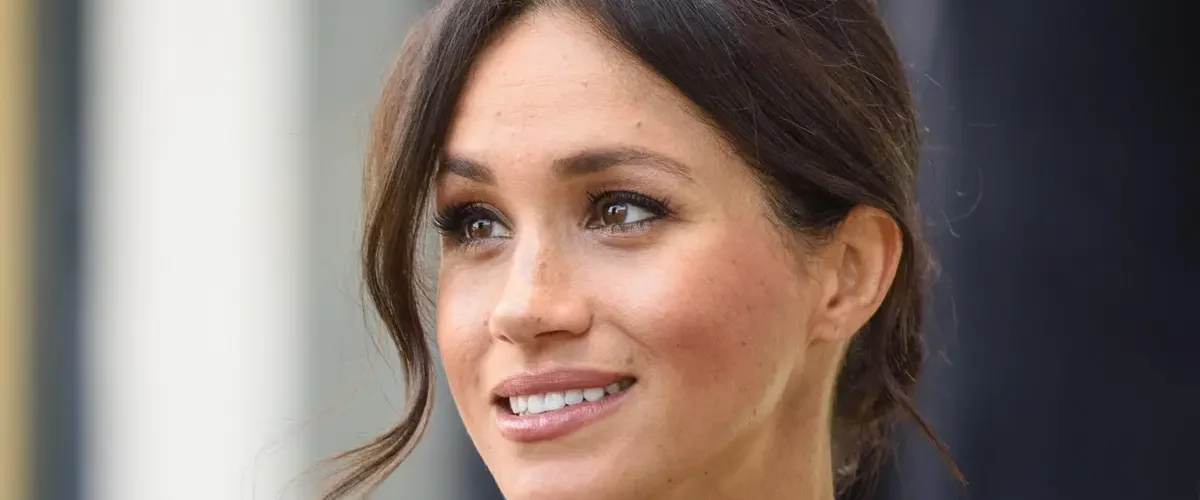
















Failed requests
These URLs were requested, but there was no response received. You will also see them in the list above.
- Domain
- ads.qaquicky.com
- URL
- https://ads.qaquicky.com/www/delivery/asyncjs.php
- Domain
- www.radiobalkanfox.com
- URL
- blob:https://www.radiobalkanfox.com/51e896c7-3dc4-48f1-a588-1d0487c6e338
- Domain
- www.youtube.com
- URL
- https://www.youtube.com/watch?v=bkQhF2ZZ2Sg&_=1
- Domain
- www.facebook.com
- URL
- https://www.facebook.com/ajax/bz?__a=1&__ccg=GOOD&__dyn=7xe6EiwgUnwn8K2Wmh0Sw8W5U4e1Fx-ewpU3WwvE3vx609vCwjE0AC0yE6u0nS4o5-0jx0Fw4Hw9O0L82Xw64w8W1uw2oEG0hi0Lo6-0o21Iw7zwtU1fE0Vy&__hs=20734.BP%3Aplugin_default_pkg.2.0...0&__hsi=7694120666009786880&__req=2&__rev=1049604663&__s=%3A%3Ax2ft47&__sp=1&__user=0&dpr=1&jazoest=22022&locale=en_US&lsd=LhVhwDvpkqOCf4eD4yzPRY
Verdicts & Comments Add Verdict or Comment
82 JavaScript Window variables
Go Pro
Only in urlscan Pro
Inspect and pivot on JavaScript variables, identifiers, and other key site metadata data with urlscan Pro. Reveal and search on client-side frameworks, runtime variables, and custom values.
Click for more information
Free trials of urlscan Pro are available.
These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.
object| 0 object| 1 function| jQuery object| _buttonizer_page_data object| _buttonizer function| gtag object| dataLayer function| fbq function| _fbq string| wpa_field_name number| wpa_unique_id string| wpa_add_test string| wpa_hidden_field function| wpa_act_as_spam function| wpa_add_honeypot_field function| wpa_add_test_block function| wpa_remove_honeypot_field object| wpa_field_info function| _createClass function| _classCallCheck function| RocketBrowserCompatibilityChecker object| RocketPreloadLinksConfig function| EvEmitter function| imagesLoaded object| addComment object| Buttonizer object| FB function| jQueryBridget function| getSize function| matchesSelector object| fizzyUIUtils function| Outlayer function| Masonry object| gridlove_js_settings function| objectFitImages object| chaty_settings function| ye function| w function| b function| J function| v object| picmo object| picmoPopup object| mejsL10n object| mejs function| MediaElement object| HtmlMediaElement function| onYouTubePlayerAPIReady function| DefaultPlayer function| MediaElementPlayer object| _wpmejsSettings object| wp function| fbAsyncInit object| React object| ReactDOM function| _ object| _wpUtilSettings function| ReactPlayer object| radioPlayer function| RadioPlayerInit object| Mailcheck object| _wpemojiSettings object| __cfBeacon object| FB_LOCAL_GLOBAL number| __DEV__ object| __buffer object| google_tag_data object| google_tag_manager string| GoogleAnalyticsObject function| ga object| twemoji object| scriptUrl object| ttPolicy object| YT object| YTConfig function| onYTReady object| gaGlobal number| 2f1acc6c3a606b082e5eef5e54414ffb string| _buttonizer_initialized object| gaplugins object| gaData boolean| radioPlayerUpdatingStreamData11 Cookies
Go Pro
Only in urlscan Pro
Review, search, and pivot on browser cookies and persistence site data to see how a site tracks users and keeps sessions alive across visits.
Click for more information
Free trials of urlscan Pro are available.
Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.
| Domain/Path | Expires | Name / Value | |||
|---|---|---|---|---|---|
| .youtube.com/ | 1969-12-31 23:59:59 |
Name: YSC Value: Na3dyjIg8cw |
|||
| .youtube.com/ | 1970-01-21 21:56:19 |
Name: VISITOR_INFO1_LIVE Value: yIJT7beklBM |
|||
| .youtube.com/ | 1970-01-21 21:56:19 |
Name: VISITOR_PRIVACY_METADATA Value: CgJJTBIEGgAgDQ%3D%3D |
|||
| .radiobalkanfox.com/ | 1970-01-21 19:46:43 |
Name: _fbp Value: fb.1.1791427067312.596436501372087179 |
|||
| .radiobalkanfox.com/ | 1970-01-22 03:13:07 |
Name: _ga_KW2XCXYMDN Value: GS2.1.s1791427067$o1$g0$t1791427067$j60$l0$h0 |
|||
| .radiobalkanfox.com/ | 1970-01-22 03:13:07 |
Name: _ga Value: GA1.2.1963039698.1791427067 |
|||
| .radiobalkanfox.com/ | 1970-01-21 17:38:33 |
Name: _gid Value: GA1.2.1011006869.1791427068 |
|||
| .radiobalkanfox.com/ | 1970-01-21 17:37:07 |
Name: _gat_gtag_UA_83585901_1 Value: 1 |
|||
| .facebook.com/ | 1970-01-21 19:46:43 |
Name: fr Value: 0dJf80FgCWOZwbEB2..BqxwH7...1.0.BqxwH7.AWdkjdLdh2b-GHkbtjDeEaXPPxQ |
|||
| .youtube.com/ | 1970-01-21 21:56:19 |
Name: __Secure-YNID Value: 22.YT=OGdxuX41X4s0Db3_e4z8kkuuFXdDM9Qsn_8OE9Qf7qdh1kjcq-HOc_2EVu_d_pJ3st3ZTGsUZENhu3OQ2qlc7cPPUJbkPLENnpVeXH4iikJp0yPWx_0GXIhfZniGb3d1JwMK76s-B1m0IVNzTPjQ_VGttZ7L8jVXxpLH_zz_qKc223TGsumjk7Mb5SzI-tkVJuTVr_S8If_BywdxduI93oI3tvDzKe5rynFHli8Le1wh6IJRu_j4otTiQl1_WApyHCqUCMffAaWA4nfUNlNoBG5K7XxgiihB6wiLfnA-dtbGadFyIo9E6Xmy3WHckdkLAeG_xGKjAfpm8DcrMDHLyQ |
|||
| .youtube.com/ | 1970-01-21 21:56:19 |
Name: __Secure-ROLLOUT_TOKEN Value: CJ_Zxc-Nvb-6pgEQnP3r77GplwMYv8mK8LGplwM%3D |
19 Console Messages
A page may trigger messages to the console to be logged. These are often error messages about being unable to load a resource or execute a piece of JavaScript. Sometimes they also provide insight into the technology behind a website.
| Source | Level | URL Text |
|---|
Indicators
This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.
ads.qaquicky.com
api.buttonizer.io
cdn.buttonizer.io
connect.facebook.net
external.ftlv21-1.fna.fbcdn.net
fonts.googleapis.com
fonts.gstatic.com
googleads.g.doubleclick.net
i.ytimg.com
img.24sata.hr
jnn-pa.googleapis.com
scontent.ftlv21-1.fna.fbcdn.net
secure.gravatar.com
static.cloudflareinsights.com
static.doubleclick.net
static.xx.fbcdn.net
www.facebook.com
www.google-analytics.com
www.google.com
www.googletagmanager.com
www.radiobalkanfox.com
www.youtube.com
ads.qaquicky.com
www.facebook.com
www.radiobalkanfox.com
www.youtube.com
104.16.80.73
142.250.154.119
142.250.154.155
142.251.13.148
142.251.13.95
142.251.14.139
142.251.151.4
142.251.153.4
142.251.155.119
142.251.20.97
157.240.0.6
172.217.116.4
172.67.146.243
172.67.71.68
192.0.73.2
192.178.183.94
45.80.89.83
57.144.244.1
91.207.22.61
004581f917268ca890df89f8b85327a2b5b9b0cc8cf1f78c6d810a0e3ae71af4
059a4ceac2ef55e9e1707329e116e850eca295235bc122c6ec8c1e08db90e1a6
063840b4b3f5869e0f0d078bab8bd29cfb3a59ee85e8e3edbbec35a8fe846fd3
0b4bf7c5a488cd14c2810925e4f27153c3d28d37f5819a58391bcafbec03270a
0d3fdd0cac9e6f287f695c740d480daa505773f699876acfe2a567f71e72f906
0e593c436776b3f6f34676659c0296c12adbea86cf421dda785e19a508c48fe4
0eda8017bee6da7050696dbfbb2f030a644804de6aa5fa9759eddf0220dda980
0fd0c3a6495430cab06abb9202ba64a371632c502eec630e45bd720483ef0874
1057419bed9d9e94af89f70f164304926800c8154277c601f30282b267c84a41
12579d8b9c28c4deffc4712d2b276a00d201d517c2c2f35b7a4f915fe1745be7
14fde1cefa375efad835cf5e386b59baa0054821a692d1be82bc49c32e6b9d08
1688410e31898cc9037678e099877bf3c5db598a486bbfb3d613d153ee704a09
18aa84579eb85b88b9e141dc67319a881c256925b538f2d6588679d392c56ac1
1a06fff62c5f0d821fb0509470cbcf0624a0fee9f759ece79ea25026a492e40d
1e1d4254072d3a4918f225cfc816ba2d0071d8172b825d4a2f903fcb5bd85c80
1fc25e512875841f628bacfa26052fa7b63ae82370a355602f468ae2c6a632ba
20b535fa80c8189e3b87d1803038389960203a886d502bc2ef1857affc2f38d2
2530057ba3fbf6cf2c7972b077e8445f60779f633dcfd9f8dee797796693c245
2595496fe48df6fcf9b1bc57c29a744c121eb4dd11566466bc13d2e52e6bbcc8
27b6404be3b9b774b2d927dbea44f19b6682738824290ad1fe80b57685af7e05
28213d52810cbbcb8855b8f6536d56acec81477431b0bee68bc746f725bfcc7e
2a99238496ca0db29d9bd0c9553000c7338491c3d480a0d035f70004dccdb632
2ad082a4d0bfbf522fa47fe0b24b1501d8b511f8919843d9ba6f1002715a2945
2be437b80ce46aa19c336211fe35b6ee3cb2d722fdee8926f0ad9b8a13bfd249
2ce4c328574a09b6a8761e998e4d91647d45b723b22e8c0f7240fe82d494e548
2da8b98551be74a3777b3eb2685e0fe1fc4325a68220cf21ca0db3f738d77264
2e10d353ff038c2cad3492fc17801af3e6ef2669c9e9713bdb78b1dcb104c4fe
2ece87cdecc00f66d265a12b3acd37602237d35e2ab21fa28609f2c95b2f6731
2fe622c5832f7bc0ec58998dd77b84b5b9e91644f390ef7e3a962858fa1cb2b8
3419282aafe2f6a01432a0180e80b47040b2c7e665a7e8f41472deafbf8061fc
35f4f974f4b2bcd44da73963347f8952e341f83909e4498227d4e26b98f66f0d
361385d647bb8b1f81f16edccfcbc22c77001e2b647b76f2c8efe4a2a3b54a21
3a5797f440bc67b59830cad81e59a71011e35cb45ed7f747b61a69b0a9b0d6ae
3b5bf9d3b0be88ce0af8a4caa7234ac4b8869ef909ce9433f1c74700bdf35847
3e5bc7ca508f5d5aa7255341243840c8d2b70c8aea323800b51610df3f5a8a2c
4371600b06b9df6aa78740b036d50aaed729a35e5540d476979aebb9f06461fd
4aef32ce247d2d4729886794194a7709041c849d7c7c79f3e100bcf0052f9345
4ca54769d43c0e26aac56b45d1019aaac17ef063ecda4c9541f0267d7151c9d3
4e894a6e908c979edbd1b7d4dc13755c9d415e95606ecb4e0e27ade365456eaa
4fc6a90fa4c979e97c66c1b4e31dfabe19fde871efad21a61b69269de112d80d
5083905862c2b7aa8a84c4f2313d359d2288fb25fbe1ff577fa7325eff2ed2d9
5274f11e6fb32ae0cf2dfb9f8043272865c397a7c4223b4cfa7d50ea52fbde89
5328a56b1d9737fb1827e8a3a961af03a5ea5a1bbd81fb51ddf488dbb33bdd82
548b66b6c3794c5beb523d1989b0cc9eb8754540f4b3888abde5d33df2a2e107
561334fb61409284cd9fd1e30131a2c9e25ae9db87babb56a037c572e31c78cf
5759bdacffdba2832ddaf6d5e8f15caad3090a7589e912a20e9c13186d4f4841
58d40748729e2b2ba21951b2a854689da3510cc9c7a884bf93aa57a3155cf58f
5a1f160f084e3df2204c807c3acd90031588164bc6056ad20d9b65d6463330de
5bcb67804579dea7aa745f5d98893308eaa592603f402a2525952dabfebf1ebd
5feceb66ffc86f38d952786c6d696c79c2dbc239dd4e91b46729d73a27fb57e9
61ccb2ff314af4b300014f1715b9e9b29f6aede9f25151e00722d5a4455c0ff2
6414232b68b9798c177c1217cb71a7c6e877bc0abc84d0a1cb3d0aa290b6b23c
6860a3de7fa2401cc24007fce35d1e5fbd58846de5e1cc98c5d77aa921e6dc31
6d161e98e47ae150b51211443eef37040fb6269dcf85ad2048548066dca99e6f
6dd3f41e70cb1e8ba8948a66a275d05c25ebd5a4dc0f15f5a087eff6478ecfb9
722a90d42ef2bd0ea38f0fdac6b4c0523aa4a027e9ffe889972100746e165582
73a1bb41497a31d4d6f71bc2d98543acd86d992d680b33fb0afe000c4c0ae8e1
74f137b628344487ecd9b95e6eb007214b4ed0239838b96c3695a4493f99964d
7557201b68fe9c7da0b95325d667217adf2a697ee646d9ec9d2b8850fcde7795
75fa193c6320eb6e00616ce18bfd934ee82c89f53904020ae819edf23484978f
7638bd9c06c31aa2bb1f20e7ae33864cafbe8225533540339bde179f968c5719
79cb399203843f65199bec32bc4abac5dfd20f141d3e4ec1424bf00c7108fa45
7d0a8eabd714b656c3ec56d4b5dfbdbbffe5ccef38067c8460d54ebcc4e0ed8d
7d2efbf28b8f8882617ef4a22d39e9708d335530734595b877d5e62146a86ab3
7e402704bfb3eb92fde399258b04c8ef0b75b2d29e73d04f7dfe41eaf3602101
7e7d81a09a47d0726c0de06e37e162c4b83fc2b1a4a5f5962fb5c29840183421
7ef48ad1c8ca628bdcc3b93a1345795525fb441d65a3c0055e5f8fb41eb5a3b0
7f0aaea04b57274e72cb4d2d9992ebd5b15eaf757098ea23d6c974f185cacec5
811e1d5a3836a96efc7f7503d8c82f28c9c9d604689ad2c31670f759ee5ee280
8586cdf45ec15714a9d939dc91eafd1a0226f640355a04bd0f53a27ba455d97f
8aa496f29312a851197faa02fadbbbdc1c8b52cff7f402193af4bb1e30e39e04
8de1569888fb20a689a4fc8a6883b7e8ed04a8a73f681ce9212c1f4306a9a270
8e2d8db61eb52731edd67ddac492a5d456133f01d252f64903ea63b8ceccbad1
8efd7ef0887f8d97df1f68248a4d6f603ab11021a0f683e61584227ee7a71909
900f2dd9f6b66295a51f90c15a9271145b7964d8032725b4647ac44b409ceffa
91432b2767de0dd8f4853e8617b55b311980c517bbb11bba08f8a2fc75650759
918b7dc3e2e2d015c16ce08b57bcb64d2253bafc1707658f361e72865498e537
95ae4b0d5c59b9842215667f5abfc45a622129e170650ebd9767759960455dcb
96605a206e257283aa31525814d046c5a492684178852aef506bcc3918d3452d
99a2c5df55c441c6f8c8128ecff43b40fdce18bc20a82af74ea4aa3bfa80ba0c
9aedcb8e1c303601c6a0248dd70634a5c744070a13a4179596da251748b089e6
9c5694d541bc0ecce9d203117d0ae57a34fa7a30859fcbd0fa603981e2f3f709
9c92ea8603874fd1c0422cbd0fa1d954e61ff76bfb41ef0b7da95d9424848954
9d105532b10ffe64f4dd076d7dbb8784e3abfe6d1ec8fc26cfe13ec5684a408d
a420c631c37e423fb5280e65a60206d4d64020080e8a8b3f8603bd308a79fe6a
a86fc1634b42ceeadfc33e8a935a58574219b42385ed753ef9aa177d4e22cef1
ad55816ac6c62f214e60a1913ff4f0215ab329034cbc7436a5514941449ca7b9
af803579d32cd83443cfd0112c66a5c1f5a276a1527dd6ec81415a7fce5c8018
b0a78b24e23311f831ad5090303244690fff1c3d41fb90247de0a6dae1c0ae88
b15c3ea03d50c2430490e7416733a254feea4237bb60b54181bd3473ebe4149f
b401dd70f2cc48c928d15a05fbd6575541104b19ac0dca6ca91948344aa52b9f
b47e3c8a088ddf9b691acfcbc7a451a7d0e3f34ef4fc689240f168af270d75f9
b63a77585832975f67c167c3e1a3c39209f3ca788cf581d802d702be954567dd
b65b3de1bc923b9355248a0d941a0eaee15dfb9a6b8eadb51323a8df6189dcd1
b700788577f5fafd9ba3f5d0481d2d33201d49dad0184af7878e6a916715b934
b7908a015a567ec2363011df2475368dbff34360e9da3fdff50604d6395fb646
c2dcf46501a48a87a7859596834012e81569a181f7b80bda4d91b04798f84751
c2e606e1fc82ea3a554aad5d0520e25d2677b89a891dc5c49e7ace08fce92e25
c447dd7677b419db7b21dbdfc6277c7816a913ffda76fd2e52702df538de0e49
c84131ecca20ee784e2c5a741fc51837a178329159ebb662136cdc497a562144
cb6f2d32c49d1c2b25e9ffc9aaafa3f83075346c01bcd4ae6eb187392a4292cf
cbdf0712673ad94781b25c743f49d8d6135f59d76ec1c9e060b4b2e259aeb28d
cd26f29d0533cedaa5f82ae8922943a51822e151374dfe19502208e6f86b37f7
cd981e302602bcf92229b11407646ce6f818fda3331209a4bce1653e47bcb82d
cee62c785268a0323cd9204be7763d45a08344201cb5435d747cb74483a8a750
d6c0276351e9a8622f9c96ce168a68837460ec615a06b39fc39a1706a4282233
d7d5e54ad1e33d7ab49c664323ced79cb9723ff15e9764cd0edc3e15208e8336
d949f1c3687aedadcedac85261865f29b17cd273997e7f6b2bfc53b2f9d4c4dd
dede012563c945321fbe3952281658f48ee6bda0531c3301bc82e28efc01421f
e00add38134eac2fb8e8e9c09cbfff7bbe57952b210322eb2eecb0a21fc055eb
e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
e6ee9431b8e9800be2ca280db3a6cd9918cc03017960fa4d5867f245feb66049
e8615ce6627972bd2099b8c4c1d024e3252b1630d7bceea433b855c3d54fd833
e9c692d6017800e26e11336b25c65c7a3fcb12833c81872f61fadbc74697ddb5
ea0c581d9c9c44b8bfd16abbcbb071a9f36a5b81863277a50ac7329a784353a5
eb28278c0c24ef171fd52d515414d6f4c4fe18d7a7e047048511b1b86abf927f
ec264e73a67355ac50685bd34a62852d8db06bfb03aeca9e88119ef1b9dea72e
eed0dc1fdb5d97ed188ae16fd5e1024a5bb744af47340346be2146300a6c54b9
efbf0b73c0766e4ded1c2683104c3332f22d9e6ffbaadfcce5e8a293f274e900
f075d71e762b285099725eb5445d91780080fa5300279fa6ad45470224b479b2
f11022379b1ba39fa3df736a39d4e3ffe249be713ffb302b600fa13faf1c03a3
f161391ebfba43d58bd4747588d9680ccfc6acb317a24cf2c49cce9a5e3275e3
f1a61277e3f902f50ab42015d8b07218db9b7601bb0967e54a52bfdcb4fa7e81
f2cc60607c1d407e194dddc628e9fde74e56b9a60c4ba39d6b17a5e2629c83fb
f39999e839e6324c9ab819e854b6c304894b0ef9c7950b53a0926a5102fa60c2
f51448b0b7f024d139fb7598d21b4e06e8174268ac93fc26cc2d4196144cb672
f65e4cc023578b2bb3522d09231cd56eb84d209b18d501eeebf8a0b098f7635e
fc774906082b59dedcfc55b8ef127783b6d056578ff4586a8ebbdb81bbe286f1
fe17b4e7b3cfea473fec7b9fa0969c0f4848e850b3bd42d5b88410e5083e53ca