
barnstablemassage.com
172.67.157.114
Public Scan
Open in
urlscan Pro
https://ufo-bass.com/ 4yr old
Effective URL:
https://barnstablemassage.com/ 3yr old
Submission: On October 11 via api (October 11th 2026, 7:38:15 am UTC) from ID — Scanned from DE Go Pro
Only in urlscan Pro
- Select different country locations for Private Scans.
- Use a global network of additional scanning locations and residential IPs for scanning.
- Interact with pages while you are scanning them.
- Download files from remote websites.
- Scan websites on the Tor Network.
Summary
TLS certificate: Issued by YE2 on October 10th 2026. Valid for: 3mo.
This is the only time barnstablemassage.com was scanned on urlscan.io!
urlscan.io Verdict: No classification
Domain & IP information
| IP Address | AS Autonomous System | ||
|---|---|---|---|
| 1 2 | 188.114.96.3 188.114.96.3 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 3 | 172.67.157.114 172.67.157.114 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 2a00:1450:400... 2a00:1450:4001:c15::5f | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 15 | 188.114.97.3 188.114.97.3 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 2 | 2606:4700::68... 2606:4700::6811:d005 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 2 | 2a00:1450:400... 2a00:1450:4001:c25::5f | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 3 | 104.17.24.14 104.17.24.14 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 3 | 2a04:4e42::411 2a04:4e42::411 | 54113 (FASTLY) (FASTLY - Fastly) | |
| 1 | 2600:1901:0:6... 2600:1901:0:658b:: | 396982 (GOOGLE-CL...) (GOOGLE-CLOUD-PLATFORM - Google LLC) | |
| 1 | 178.128.116.123 178.128.116.123 | 14061 (DIGITALOC...) (DIGITALOCEAN-ASN - DigitalOcean) | |
| 2 | 2606:4700::68... 2606:4700::6810:5049 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 2 | 57.144.244.128 57.144.244.128 | 32934 (FACEBOOK) (FACEBOOK - Facebook) | |
| 1 | 2606:4700:10:... 2606:4700:10::ac42:8c49 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 3 | 142.251.110.94 142.251.110.94 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 2 | 2a06:98c1:312... 2a06:98c1:3121::3 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 2620:127:f00e... 2620:127:f00e:ff00:: | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 193.34.76.44 193.34.76.44 | 205212 (CRYOUS-NE...) (CRYOUS-NETWORKS LoudTronix Inc.) | |
| 1 1 | 2606:4700::68... 2606:4700::6810:344e | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 2 | 2606:4700::68... 2606:4700::6810:8dd1 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 2606:4700:440... 2606:4700:4404::ac40:9310 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 2 | 2606:4700::68... 2606:4700::6810:6dfe | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 2606:4700::68... 2606:4700::6810:a0a8 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 2606:4700::68... 2606:4700::6811:5cbb | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 1 | 104.18.80.204 104.18.80.204 | 13335 (CLOUDFLAR...) (CLOUDFLARENET - Cloudflare) | |
| 59 | 24 |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| ufo-bass.com 4yr old | |
| aplo-evnt.com 3yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| barnstablemassage.com 3yr old |
ASN15169 (GOOGLE - Google LLC, US)
| fonts.googleapis.com 10yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| outerbloom.com 10yr old | |
| meubelkayumurah.pics 4yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| cdn.jsdelivr.net 14yr old |
ASN15169 (GOOGLE - Google LLC, US)
| ajax.googleapis.com 10yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| cdnjs.cloudflare.com 14yr old |
ASN396982 (GOOGLE-CLOUD-PLATFORM - Google LLC, US)
| cdn.shopify.com 14yr old |
ASN14061 (DIGITALOCEAN-ASN - DigitalOcean, LLC, US)
| gen.blackmolesamp.com 5mo old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| static.cloudflareinsights.com 7yr old |
ASN32934 (FACEBOOK - Facebook, Inc., US)
PTR: xx-fbcdn-shv-01-fra5.fbcdn.net
| connect.facebook.net 14yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| assets.apollo.io 6yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: bz-in-f94.1e100.net
| fonts.gstatic.com 10yr old |
ASN205212 (CRYOUS-NETWORKS LoudTronix Inc., CA)
PTR: localtunnel.app
| googlesignintest.loca.lt 5yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| api-na1.hubapi.com 6yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| js-na2.hs-scripts.com 2yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| js-na2.hs-banner.com 2yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| js-na2.hscollectedforms.net 2yr old | |
| forms-na2.hscollectedforms.net 2yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| js-na2.hs-analytics.net 2yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| track-na2.hubspot.com 2yr old |
ASN13335 (CLOUDFLARENET - Cloudflare, Inc., US)
| forms-na2.hsforms.com 2yr old |
| Apex Domain Subdomains |
Transfer | |
|---|---|---|
| 13 |
outerbloom.com
outerbloom.com — Cisco Umbrella Rank: 486373 10yr old |
143 KB |
| 3 |
aplo-evnt.com
aplo-evnt.com — Cisco Umbrella Rank: 19932 3yr old |
2 KB |
| 3 |
gstatic.com
fonts.gstatic.com — Cisco Umbrella Rank: 31 10yr old |
43 KB |
| 3 |
jquery.com
code.jquery.com — Cisco Umbrella Rank: 891 13yr old |
108 KB |
| 3 |
cloudflare.com
cdnjs.cloudflare.com — Cisco Umbrella Rank: 295 14yr old |
68 KB |
| 3 |
googleapis.com
fonts.googleapis.com — Cisco Umbrella Rank: 43 10yr old ajax.googleapis.com — Cisco Umbrella Rank: 653 10yr old |
63 KB |
| 3 |
barnstablemassage.com
barnstablemassage.com 3yr old |
60 KB |
| 2 |
hscollectedforms.net
js-na2.hscollectedforms.net — Cisco Umbrella Rank: 22127 2yr old forms-na2.hscollectedforms.net — Cisco Umbrella Rank: 22282 2yr old |
28 KB |
| 2 |
hs-scripts.com
js-na2.hs-scripts.com — Cisco Umbrella Rank: 13918 2yr old |
1 KB |
| 2 |
facebook.net
connect.facebook.net — Cisco Umbrella Rank: 234 14yr old |
118 KB |
| 2 |
cloudflareinsights.com
static.cloudflareinsights.com — Cisco Umbrella Rank: 304 7yr old |
21 KB |
| 2 |
meubelkayumurah.pics
meubelkayumurah.pics — Cisco Umbrella Rank: 113588 4yr old |
272 KB |
| 2 |
jsdelivr.net
cdn.jsdelivr.net — Cisco Umbrella Rank: 285 14yr old |
23 KB |
| 1 |
hsforms.com
forms-na2.hsforms.com — Cisco Umbrella Rank: 23617 2yr old |
665 B |
| 1 |
hubspot.com
track-na2.hubspot.com — Cisco Umbrella Rank: 14970 2yr old |
985 B |
| 1 |
hs-analytics.net
js-na2.hs-analytics.net — Cisco Umbrella Rank: 14512 2yr old |
43 KB |
| 1 |
hs-banner.com
js-na2.hs-banner.com — Cisco Umbrella Rank: 14506 2yr old |
24 KB |
| 1 |
hubapi.com
1 redirects
api-na1.hubapi.com — Cisco Umbrella Rank: 45571 6yr old |
901 B |
| 1 |
loca.lt
googlesignintest.loca.lt 5yr old |
|
| 1 |
shop.app
shop.app — Cisco Umbrella Rank: 2602 8yr old |
180 KB |
| 1 |
apollo.io
assets.apollo.io — Cisco Umbrella Rank: 18336 6yr old |
3 KB |
| 1 |
blackmolesamp.com
gen.blackmolesamp.com — Cisco Umbrella Rank: 730077 5mo old |
3 MB |
| 1 |
shopify.com
cdn.shopify.com — Cisco Umbrella Rank: 1836 14yr old |
2 KB |
| 1 |
ufo-bass.com
1 redirects
ufo-bass.com 4yr old |
467 B |
| 0 |
ngrok.io
Failed
e9e1-180-254-64-204.ngrok.io Failed 5yr old 14e1-180-254-64-204.ngrok.io Failed 5yr old 6403-180-254-64-204.ngrok.io Failed 5yr old |
|
| 59 | 25 |
| Domain | Requested by | |
|---|---|---|
| 13 | outerbloom.com |
barnstablemassage.com
outerbloom.com |
| 3 | aplo-evnt.com |
assets.apollo.io
|
| 3 | fonts.gstatic.com |
fonts.googleapis.com
|
| 3 | code.jquery.com |
barnstablemassage.com
|
| 3 | cdnjs.cloudflare.com |
barnstablemassage.com
|
| 3 | barnstablemassage.com |
barnstablemassage.com
static.cloudflareinsights.com |
| 2 | js-na2.hs-scripts.com |
js-na2.hs-analytics.net
|
| 2 | connect.facebook.net |
barnstablemassage.com
connect.facebook.net |
| 2 | static.cloudflareinsights.com |
barnstablemassage.com
|
| 2 | meubelkayumurah.pics |
barnstablemassage.com
|
| 2 | ajax.googleapis.com |
barnstablemassage.com
|
| 2 | cdn.jsdelivr.net |
barnstablemassage.com
|
| 1 | forms-na2.hsforms.com | |
| 1 | forms-na2.hscollectedforms.net |
js-na2.hscollectedforms.net
|
| 1 | track-na2.hubspot.com | |
| 1 | js-na2.hs-analytics.net |
api-na1.hubapi.com
|
| 1 | js-na2.hscollectedforms.net |
api-na1.hubapi.com
|
| 1 | js-na2.hs-banner.com |
api-na1.hubapi.com
|
| 1 | api-na1.hubapi.com | 1 redirects |
| 1 | googlesignintest.loca.lt |
barnstablemassage.com
|
| 1 | shop.app |
outerbloom.com
|
| 1 | assets.apollo.io |
barnstablemassage.com
|
| 1 | gen.blackmolesamp.com |
barnstablemassage.com
|
| 1 | cdn.shopify.com |
barnstablemassage.com
|
| 1 | fonts.googleapis.com |
barnstablemassage.com
|
| 1 | ufo-bass.com | 1 redirects |
| 0 | 6403-180-254-64-204.ngrok.io Failed |
barnstablemassage.com
|
| 0 | 14e1-180-254-64-204.ngrok.io Failed |
barnstablemassage.com
|
| 0 | e9e1-180-254-64-204.ngrok.io Failed |
barnstablemassage.com
|
| 59 | 29 |
This site contains no links.
| Subject Issuer | Validity | Valid | |
|---|---|---|---|
| barnstablemassage.com YE2 |
2026-10-10 - 2027-01-08 |
3mo | crt.sh |
| upload.video.google.com WE2 |
2026-09-18 - 2026-12-11 |
3mo | crt.sh |
| outerbloom.com YE1 |
2026-09-24 - 2026-12-23 |
3mo | crt.sh |
| *.jsdelivr.net Sectigo Public Server Authentication CA DV R36 |
2026-04-22 - 2026-11-06 |
7mo | crt.sh |
| cdnjs.cloudflare.com WE1 |
2026-09-07 - 2026-12-06 |
3mo | crt.sh |
| *.jquery.com Sectigo Public Server Authentication CA DV E36 |
2026-05-20 - 2026-12-04 |
7mo | crt.sh |
| cdn.shopify.com YR1 |
2026-09-12 - 2026-12-11 |
3mo | crt.sh |
| meubelkayumurah.pics WE1 |
2026-09-06 - 2026-12-05 |
3mo | crt.sh |
| gen.blackmolesamp.com YE1 |
2026-08-30 - 2026-11-28 |
3mo | crt.sh |
| cloudflareinsights.com WE1 |
2026-08-14 - 2026-11-12 |
3mo | crt.sh |
| *.facebook.com DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
2026-07-20 - 2026-10-18 |
3mo | crt.sh |
| apollo.io YE1 |
2026-10-09 - 2027-01-07 |
3mo | crt.sh |
| *.gstatic.com WE2 |
2026-09-18 - 2026-12-11 |
3mo | crt.sh |
| aplo-evnt.com WE1 |
2026-09-23 - 2026-12-22 |
3mo | crt.sh |
| shop.app WE1 |
2026-09-02 - 2026-12-01 |
3mo | crt.sh |
| loca.lt YE2 |
2026-09-09 - 2026-12-08 |
3mo | crt.sh |
| hs-banner.com WE1 |
2026-09-04 - 2026-12-03 |
3mo | crt.sh |
| hscollectedforms.net WE1 |
2026-09-02 - 2026-12-01 |
3mo | crt.sh |
| hs-analytics.net WE1 |
2026-09-15 - 2026-12-14 |
3mo | crt.sh |
| hs-scripts.com WE1 |
2026-09-05 - 2026-12-04 |
3mo | crt.sh |
| hubspot.com WE1 |
2026-09-11 - 2026-12-10 |
3mo | crt.sh |
| hsforms.com WE1 |
2026-08-23 - 2026-11-21 |
3mo | crt.sh |
This page contains 2 frames:
Primary Page:
https://barnstablemassage.com/
Frame ID: 93C53B8894EBFB2F1B1B66782124EC7E
Requests: 53 HTTP requests in this frame
Frame:
https://shop.app/pay/hop?analytics_trace_id=599caf8f-a535-4fd5-b54f-fa043128f782&target_origin=https%3A%2F%2Fbarnstablemassage.com&client_handle=outerbloom1.myshopify.com
Frame ID: 9A6EB4FCB56F3A00912B701122ABEACA
Requests: 4 HTTP requests in this frame
Screenshot
Go Pro
Only in urlscan Pro
Use the Visual Search feature to find pages with visually similar screenshots.
Click for more information
Free trials of urlscan Pro are available.
Page Title
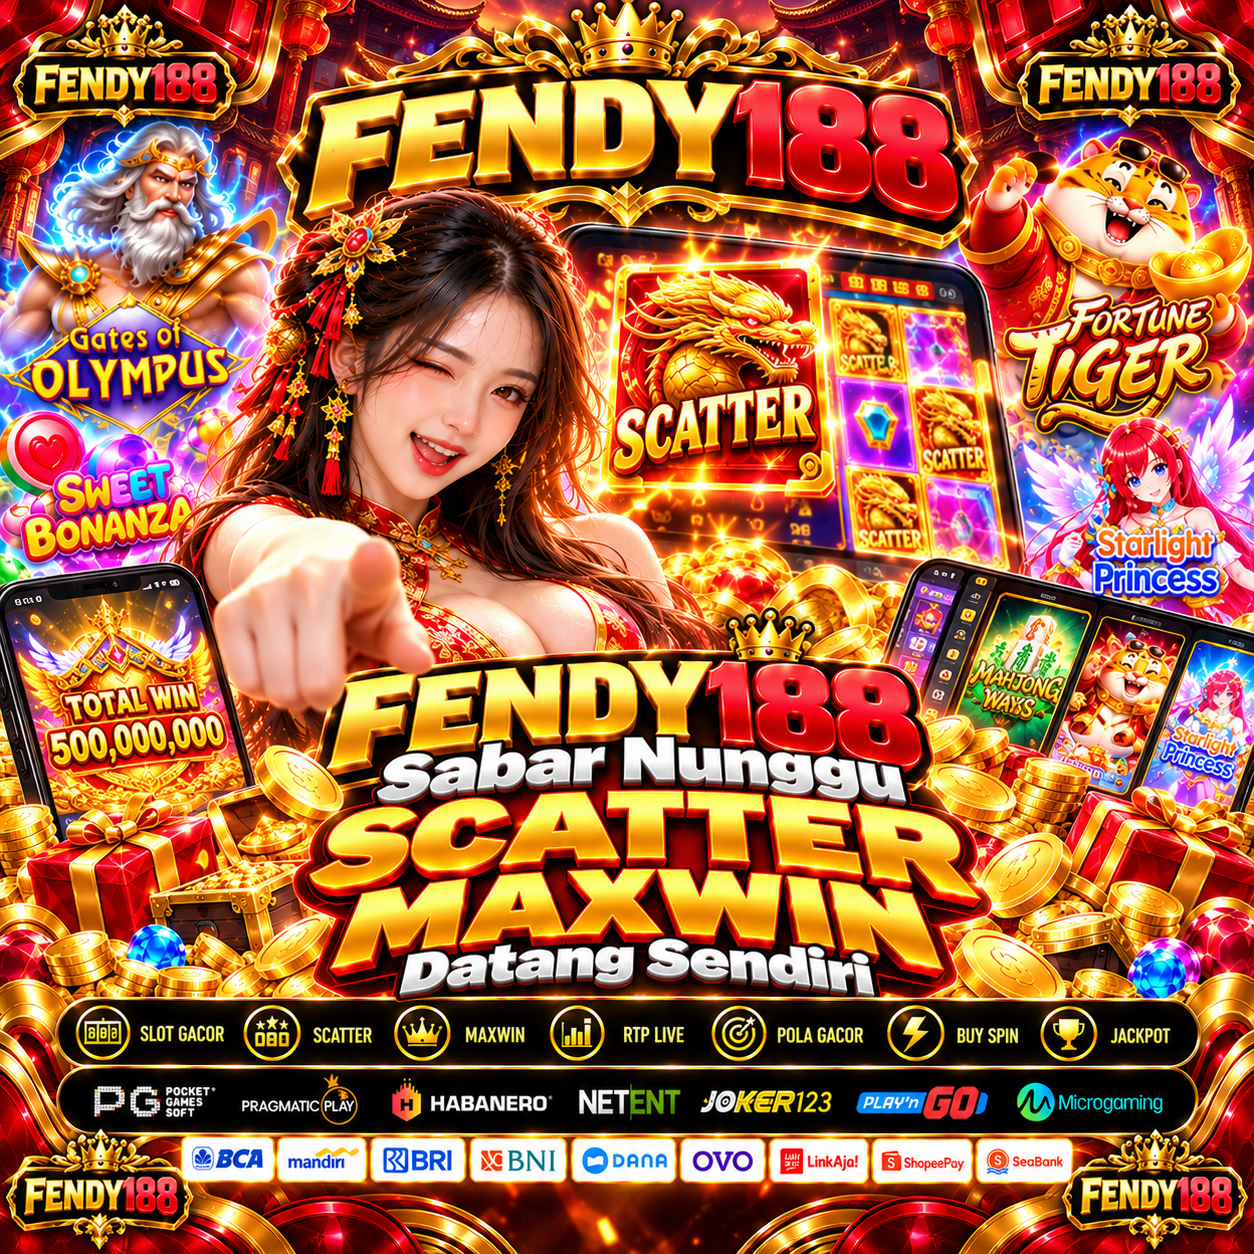
FENDY188: Sabar Nunggu Scatter, Maxwin Datang SendiriPage URL History
Go Pro
Only in urlscan Pro
Search our real-time database of newly observed domains and
hostnames. Pivot on different attributes, and setup keyword alerts for
newly observed domains.
Click for more information
Free trials of urlscan Pro are available.
Show full URLs
-
https://ufo-bass.com/
HTTP 301
https://barnstablemassage.com/ Page URL
Detected technologies
 Shopify
(Ecommerce)
Expand
Detected patterns
- cdn\.shopify\.com
 WordPress
(CMS)
Expand
Detected patterns
- /wp-(?:content|includes)/
 AMP
(JavaScript frameworks)
Expand
Detected patterns
- <link rel="amphtml"
 cdnjs
(CDN)
Expand
Detected patterns
- cdnjs\.cloudflare\.com
 Cloudflare Bot Management
(Security)
Expand
Detected patterns
Cloudflare Browser Insights
(Analytics)
Expand
Detected patterns
- static\.cloudflareinsights\.com/beacon(?:\.min)?\.js
 Facebook Pixel
(Analytics)
Expand
Detected patterns
- connect\.facebook\.\w+/.+/fbevents\.js
- connect\.facebook.\w+/signals/config/\d+\?v=([\d\.]+)
 Font Awesome
(Font scripts)
Expand
Detected patterns
- (?:F|f)o(?:n|r)t-?(?:A|a)wesome(?:.*?([0-9a-fA-F]{7,40}|[\d]+(?:.[\d]+(?:.[\d]+)?)?)|)
 Google Hosted Libraries
(CDN)
Expand
Detected patterns
- ajax\.googleapis\.com/ajax/libs/
 HubSpot
(Marketing automation)
Expand
Detected patterns
- \.hs-scripts\.com/
 jQuery
(JavaScript libraries)
Expand
Detected patterns
- jquery
- /(\d+\.\d+\.\d+)/jquery(?!\.popupoverlay\.js|(?:\.[\w-]*)*fancybox)[/.-][^u]
- /jquery(?:-(\d+\.\d+\.\d+))[/.-]
jQuery CDN
(CDN)
Expand
Detected patterns
- code\.jquery\.com/
 jQuery UI
(JavaScript libraries)
Expand
Detected patterns
- ([\d.]+)/jquery-ui(?:\.min)?\.js
- jquery-ui.*\.js
 jsDelivr
(CDN)
Expand
Detected patterns
- cdn\.jsdelivr\.net
 Select2
(JavaScript libraries)
Expand
Detected patterns
- select2(?:\.min|\.full)?\.js
Page Statistics
0 Outgoing links
Go Pro
Only in urlscan Pro
Effortlessly use any on-page link as a pivot to discover other pages pointing to the exact same destination. Seamlessly trace both specific URLs and broader domains to uncover hidden connection networks and map out backlink relationships with ease.
Click for more information
Free trials of urlscan Pro are available.
These are links going to different origins than the main page.
Page URL History
This captures the URL locations of the websites, including HTTP redirects and client-side redirects via JavaScript or Meta fields.
-
https://ufo-bass.com/
HTTP 301
https://barnstablemassage.com/ Page URL
Redirected requests
There were HTTP redirect chains for the following requests:
Request Chain 47- https://api-na1.hubapi.com/scriptloader/v1/6800477.js?shop=outerbloom1.myshopify.com HTTP 307
- https://js-na2.hs-scripts.com/6800477.js
59 HTTP transactions
Go Pro
Only in urlscan Pro
Inspect WebSocket connections, examine POST data effortlessly, and track overlap counts in real time. Features live search and filtering across all HTTP output, complete with full response metadata for deep analysis.
Click for more information
Free trials of urlscan Pro are available.
3 data transactions
| Method Protocol |
Status | Resource Path |
Size x-fer |
Time Latency |
Type MIME-Type |
IP Location |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
|
GET H3 |
200 |
Primary Request
/
Show response
barnstablemassage.com/ Redirect Chain
|
720 KB 59 KB |
243ms
212ms |
Document
text/html |
172.67.157.114 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
css
fonts.googleapis.com/ |
10 KB 1 KB |
50ms
20ms |
Stylesheet
text/css |
2a00:1450:4001:c15::5f Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
wishlist-styles.css
outerbloom.com/cdn/shop/t/138/assets/ |
1 KB 1 KB |
50ms
23ms |
Stylesheet
text/css |
188.114.97.3 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
select2.min.css
cdn.jsdelivr.net/npm/select2@4.1.0-rc.0/dist/css/ |
16 KB 3 KB |
42ms
14ms |
Stylesheet
text/css |
2606:4700::6811:d005 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
jquery.min.js
Show response
ajax.googleapis.com/ajax/libs/jquery/3.6.4/ |
88 KB 31 KB |
38ms
8ms |
Script
text/javascript |
2a00:1450:4001:c25::5f Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
jquery-ui.min.js
Show response
cdnjs.cloudflare.com/ajax/libs/jqueryui/1.13.2/ |
249 KB 56 KB |
38ms
26ms |
Script
application/javascript |
104.17.24.14 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
qrcode.min.js
Show response
cdnjs.cloudflare.com/ajax/libs/qrcodejs/1.0.0/ |
19 KB 7 KB |
40ms
39ms |
Script
application/javascript |
104.17.24.14 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
select2.min.js
Show response
cdn.jsdelivr.net/npm/select2@4.1.0-rc.0/dist/js/ |
71 KB 20 KB |
40ms
12ms |
Script
application/javascript |
2606:4700::6811:d005 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
vissense.js
Show response
cdnjs.cloudflare.com/ajax/libs/vissense/0.9.0/ |
22 KB 5 KB |
19ms
18ms |
Script
application/javascript |
104.17.24.14 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
combine.min.css
outerbloom.com/cdn/shop/t/138/assets/ |
159 KB 21 KB |
54ms
28ms |
Stylesheet
text/css |
188.114.97.3 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
font-awesome.css
outerbloom.com/cdn/shop/t/138/assets/ |
30 KB 7 KB |
50ms
24ms |
Stylesheet
text/css |
188.114.97.3 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
jquery-ui.min.css
code.jquery.com/ui/1.13.0/themes/base/ |
30 KB 7 KB |
42ms
16ms |
Stylesheet
text/css |
2a04:4e42::411 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
jquery-1.12.4.min.js
Show response
code.jquery.com/ |
95 KB 33 KB |
33ms
7ms |
Script
application/javascript |
2a04:4e42::411 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
combine.js
Show response
outerbloom.com/cdn/shop/t/138/assets/ |
117 KB 29 KB |
49ms
24ms |
Script
text/javascript |
188.114.97.3 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
jquery-ui.min.js
Show response
code.jquery.com/ui/1.13.0/ |
249 KB 67 KB |
32ms
6ms |
Script
application/javascript |
2a04:4e42::411 Fastly |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
404 |
preloads.js
barnstablemassage.com/checkouts/internal/ |
0 0 |
231ms
229ms |
Script
text/html |
172.67.157.114 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
client.init-shop-cart-sync_BLuSqYWl.en.esm.js
Show response
outerbloom.com/cdn/shopifycloud/shop-js/modules/v2/ |
1003 B 1 KB |
51ms
26ms |
Script
text/javascript |
188.114.97.3 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
chunk.common_DplD2_3Q.en.esm.js
Show response
outerbloom.com/cdn/shopifycloud/shop-js/modules/v2/ |
161 KB 49 KB |
43ms
18ms |
Script
text/javascript |
188.114.97.3 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
chunk.modal_BxEbAqG6.en.esm.js
Show response
outerbloom.com/cdn/shopifycloud/shop-js/modules/v2/ |
28 KB 11 KB |
47ms
22ms |
Script
text/javascript |
188.114.97.3 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
load_feature-a0a9edcb.js
Show response
outerbloom.com/cdn/shopifycloud/storefront/assets/storefront/ |
13 KB 4 KB |
21ms
19ms |
Script
text/javascript |
188.114.97.3 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
app.css
cdn.shopify.com/extensions/019b5a94-a328-79ac-9b0a-d9abe0913c8c/bitbybit-google-signin-136/assets/ |
10 KB 2 KB |
43ms
12ms |
Stylesheet
text/css |
2600:1901:0:658b:: Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
shopify-perf-kit-3.1.0.min.js
Show response
outerbloom.com/cdn/shopifycloud/perf-kit/ |
55 KB 19 KB |
20ms
18ms |
Script
text/javascript |
188.114.97.3 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
logo-fendy188.png
meubelkayumurah.pics/wp-content/uploads/2026/05/ |
57 KB 58 KB |
59ms
34ms |
Image
image/png |
188.114.97.3 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
2-1791615750474-d414be1c7382.png
gen.blackmolesamp.com/uploads/ |
3 MB 3 MB |
517ms
166ms |
Image
image/png |
178.128.116.123 DigitalOcean |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
v8c78df7c7c0f484497ecbca7046644da1771523124516
Show response
static.cloudflareinsights.com/beacon.min.js/ |
30 KB 11 KB |
33ms
31ms |
Script
text/javascript |
2606:4700::6810:5049 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
v31edd6df95cf4e85bb4c19e7a9bdbcba1788362987495
Show response
static.cloudflareinsights.com/beacon.min.js/ |
30 KB 10 KB |
36ms
16ms |
Script
text/javascript |
2606:4700::6810:5049 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
fbevents.js
Show response
connect.facebook.net/en_US/ |
419 KB 110 KB |
57ms
9ms |
Script
application/x-javascript |
57.144.244.128 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
tracker.iife.js
Show response
assets.apollo.io/micro/website-tracker/ |
5 KB 3 KB |
76ms
15ms |
Script
application/javascript |
2606:4700:10::ac42:8c49 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST |
|
collect
outerbloom.com/api/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
OPTIONS H3 |
404 |
collect
outerbloom.com/api/ Frame |
0 0 |
151ms
150ms |
Preflight
text/html |
188.114.97.3 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
6xK3dSBYKcSV-LCoeQqfX1RYOo3qOK7l.woff2
fonts.gstatic.com/s/sourcesanspro/v24/ |
14 KB 14 KB |
33ms
10ms |
Font
font/woff2 |
142.251.110.94 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
6xKydSBYKcSV-LCoeQqfX1RYOo3i54rwlxdu.woff2
fonts.gstatic.com/s/sourcesanspro/v24/ |
14 KB 14 KB |
32ms
10ms |
Font
font/woff2 |
142.251.110.94 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
6xKydSBYKcSV-LCoeQqfX1RYOo3ig4vwlxdu.woff2
fonts.gstatic.com/s/sourcesanspro/v24/ |
14 KB 14 KB |
37ms
15ms |
Font
font/woff2 |
142.251.110.94 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
165971065669324
Show response
connect.facebook.net/signals/config/ |
31 KB 7 KB |
509ms
509ms |
Script
application/x-javascript |
57.144.244.128 |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
can_track_visitor
Show response
aplo-evnt.com/api/v1/intent_pixel/ |
19 B 2 KB |
172ms
140ms |
Fetch
application/json |
2a06:98c1:3121::3 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
400 |
track_request
Show response
aplo-evnt.com/api/v1/intent_pixel/ |
70 B 1018 B |
223ms
223ms |
Fetch
application/json |
188.114.96.3 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
OPTIONS H2 |
200 |
track_request
aplo-evnt.com/api/v1/intent_pixel/ Frame |
0 0 |
140ms
139ms |
Preflight
|
2a06:98c1:3121::3 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
hop
Show response
shop.app/pay/ Frame 9A6E |
180 KB 180 KB |
182ms
153ms |
Document
application/json |
2620:127:f00e:ff00:: Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET DATA |
200 OK |
truncated
/ Frame 9A6E |
3 KB 0 |
Image
image/png |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET DATA |
200 OK |
truncated
/ Frame 9A6E |
5 KB 0 |
Image
image/png |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET DATA |
200 OK |
truncated
/ Frame 9A6E |
155 B 0 |
Image
image/png |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST |
|
collect
outerbloom.com/api/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
OPTIONS H3 |
404 |
collect
outerbloom.com/api/ Frame |
0 0 |
156ms
156ms |
Preflight
text/html |
188.114.97.3 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
shopifyPageScript.js
e9e1-180-254-64-204.ngrok.io/public/scripts/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
jquery.min.js
Show response
ajax.googleapis.com/ajax/libs/jquery/3.5.1/ |
87 KB 30 KB |
9ms
8ms |
Script
text/javascript |
2a00:1450:4001:c25::5f Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
shopifyPageScript.js
14e1-180-254-64-204.ngrok.io/public/scripts/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
shopify-page-script.js
6403-180-254-64-204.ngrok.io/public/scripts/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H/1.1 |
503 Service Unavailable |
shopify-page-script.js
googlesignintest.loca.lt/public/scripts/ |
0 0 |
424ms
133ms |
Script
text/plain |
193.34.76.44 CRYOUS-NETWORKS L... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
6800477.js
Show response
js-na2.hs-scripts.com/ Redirect Chain
|
2 KB 1 KB |
56ms
29ms |
Script
application/javascript |
2606:4700::6810:8dd1 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST H3 |
404 |
rum
Show response
barnstablemassage.com/cdn-cgi/ |
151 B 647 B |
13ms
12ms |
XHR
text/html |
172.67.157.114 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
icon-fendy188.png
meubelkayumurah.pics/wp-content/uploads/2026/05/ |
214 KB 214 KB |
33ms
32ms |
Other
image/png |
188.114.97.3 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
banner.js
Show response
js-na2.hs-banner.com/v2/6800477/ |
67 KB 24 KB |
43ms
16ms |
Script
text/javascript |
2606:4700:4404::ac40:9310 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
collectedforms.js
Show response
js-na2.hscollectedforms.net/ |
78 KB 27 KB |
197ms
170ms |
Script
application/javascript |
2606:4700::6810:6dfe Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
6800477.js
Show response
js-na2.hs-analytics.net/analytics/1791701100000/ |
107 KB 43 KB |
50ms
17ms |
Script
text/javascript |
2606:4700::6810:a0a8 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
6800477.js
Show response
js-na2.hs-scripts.com/ |
2 KB 40 B |
24ms
23ms |
Script
application/javascript |
2606:4700::6810:8dd1 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
__ptq.gif
track-na2.hubspot.com/ |
45 B 985 B |
260ms
188ms |
Image
image/gif |
2606:4700::6811:5cbb Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
json
Show response
forms-na2.hscollectedforms.net/collected-forms/v1/config/ |
133 B 688 B |
694ms
683ms |
XHR
application/json |
2606:4700::6810:6dfe Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
counters.gif
forms-na2.hsforms.com/embed/v3/ |
35 B 665 B |
190ms
169ms |
Image
image/gif |
104.18.80.204 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST |
|
collect
outerbloom.com/api/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
OPTIONS H3 |
404 |
collect
outerbloom.com/api/ Frame |
0 0 |
153ms
152ms |
Preflight
text/html |
188.114.97.3 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
POST |
|
collect
outerbloom.com/api/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
OPTIONS H3 |
404 |
collect
outerbloom.com/api/ Frame |
0 0 |
156ms
155ms |
Preflight
text/html |
188.114.97.3 Cloudflare |
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||




Failed requests
These URLs were requested, but there was no response received. You will also see them in the list above.
- Domain
- outerbloom.com
- URL
- https://outerbloom.com/api/collect
- Domain
- outerbloom.com
- URL
- https://outerbloom.com/api/collect
- Domain
- e9e1-180-254-64-204.ngrok.io
- URL
- https://e9e1-180-254-64-204.ngrok.io/public/scripts/shopifyPageScript.js?shop=outerbloom1.myshopify.com
- Domain
- 14e1-180-254-64-204.ngrok.io
- URL
- https://14e1-180-254-64-204.ngrok.io/public/scripts/shopifyPageScript.js?shop=outerbloom1.myshopify.com
- Domain
- 6403-180-254-64-204.ngrok.io
- URL
- https://6403-180-254-64-204.ngrok.io/public/scripts/shopify-page-script.js?shop=outerbloom1.myshopify.com
- Domain
- outerbloom.com
- URL
- https://outerbloom.com/api/collect
- Domain
- outerbloom.com
- URL
- https://outerbloom.com/api/collect
Verdicts & Comments Add Verdict or Comment
35 JavaScript Window variables
Go Pro
Only in urlscan Pro
Inspect and pivot on JavaScript variables, identifiers, and other key site metadata data with urlscan Pro. Reveal and search on client-side frameworks, runtime variables, and custom values.
Click for more information
Free trials of urlscan Pro are available.
These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.
object| 0 function| $ function| jQuery function| fbq function| _fbq object| uetq function| initApollo function| _extends function| _typeof function| LazyLoad function| Swiper object| Shopify boolean| ShopifyPaypalV4VisibilityTracking function| portableWalletsHideBuyerConsent function| portableWalletsShowBuyerConsent function| ga function| QRCode function| VisSense object| __cfBeacon function| changeImage object| trackingFunctions object| _hsp string| __hsReferrer string| __hsInitialUrl object| hsCookieBanner boolean| _hspb_loaded boolean| _hspb_ran object| _hsq function| sanitizeKey boolean| _hstc_ran object| hsCallsToActionsReady string| __hsUserToken number| expireDateTime boolean| _hstc_loaded object| __hsCollectedFormsDebug12 Cookies
Go Pro
Only in urlscan Pro
Review, search, and pivot on browser cookies and persistence site data to see how a site tracks users and keeps sessions alive across visits.
Click for more information
Free trials of urlscan Pro are available.
Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.
| Domain/Path | Expires | Name / Value | |||
|---|---|---|---|---|---|
| .apollo.io/ | 1970-01-21 17:41:46 |
Name: __cf_bm Value: yC3p_wTfr2e8t4x7Pq.HspjWby7kkNMGERiyTePJFTA-1791704296.6460996-1.0.1.1-UUehWqj6zeApTjDVfhfuqJAdwNKdpA4eC1OEDIG2OphIhzfue0nLzVDFTGH.F2OaHSySBZIRIWcI.1cLB2AdCly31gvpnyTMIz28cNKRi5YDqjZamltKGxsihjQG6qcM |
|||
| .shop.app/ | 1970-01-22 02:27:20 |
Name: _shop_app_essential Value: :AaEp5e6zAAEAd13Rorn1vv3MTJhxVyEQCGZv2plCnqf1SlOEt8FVK-vOyKiX5uSvX_LHHp3EaS2epDJNW9gZiwDig7EvDosjotFctTaIryZyXi-CMlUe: |
|||
| .hubapi.com/ | 1970-01-21 17:41:46 |
Name: __cf_bm Value: NJp1x.IrLofG1y07ffzWMCYSueYYLjP1otJoSdcuP30-1791704298.570328-1.0.1.1-nsSEz9LckRFOqIDFcKdZ1bKf0BNwA7Iodj4emcxRd9zAoJmcFiwo7tXNvyiyFy3rZi4EpsAquKdvPGyuNSa._16gnUKweukqb78c3vbZUlsx1091oQfYHS4w7cgL_8Nx |
|||
| .hs-scripts.com/ | 1970-01-21 17:41:46 |
Name: __cf_bm Value: 593av2X9ixpb9pqSRoTzdN89cyLrDAk4kdMJrP5jUos-1791704299.0003178-1.0.1.1-MEQb8oOb3ydZKSZtuL1bpinIutfehjL8m8qK8YotvQR2KgEqhyX0.K8J7tgf5T1gPHpm7p.KGpRfsP3LI.CAue6yZv5hCvEI1r3_tpXAN4IGGPDQ2ekMrl_6eKx1D.TI |
|||
| .hs-banner.com/ | 1970-01-21 17:41:46 |
Name: __cf_bm Value: Ycf5ie2olVi9WNmTyTbPr00H2LtY3uSeooqHQroAMsg-1791704299.0561519-1.0.1.1-rAFHR0S39qMZXftIetdlN2wr7mESy9APzCnA89.dP_p4LgGVVJbHjAtN7hBKcDZhokVMeL8ksTHoWc_P1D522_qGqu_WWbT6v1jxPAJqxcOShhGvqGVUCHigzn9ACMWc |
|||
| .hs-analytics.net/ | 1970-01-21 17:41:46 |
Name: __cf_bm Value: MSzYn5nVDqMjS1NgfbM1b5dgHsAgsj3z4UJRzWy3KV4-1791704299.0629914-1.0.1.1-1YRyJipUAENPDlPGeRylV1G7VpQYiAUT1GtxNPXC801vt.FvUj4drKUiu_f_VuvXH9b3h0YIgwqCyiECvb0nYfc976qTDnULktK1o5aJyMw9hG5_ivM3iq_X5x3_MeFK |
|||
| barnstablemassage.com/ | 1970-01-21 22:00:56 |
Name: __hstc Value: 94039298.f7b45251ea5fc6ec945a840e326ccb05.1791704299088.1791704299088.1791704299088.1 |
|||
| barnstablemassage.com/ | 1970-01-21 22:00:56 |
Name: hubspotutk Value: f7b45251ea5fc6ec945a840e326ccb05 |
|||
| barnstablemassage.com/ | 1969-12-31 23:59:59 |
Name: __hssrc Value: 1 |
|||
| barnstablemassage.com/ | 1970-01-21 17:41:46 |
Name: __hssc Value: 94039298.1.1791704299088 |
|||
| .hubspot.com/ | 1970-01-21 17:41:46 |
Name: __cf_bm Value: lDwSWan0GHvxEGA06EqHX832dv2fAMN08qi0tmEBHDU-1791704299.1700377-1.0.1.1-1oS6wdS_iFefUEULSjrhqSmycfnNJJv68daTi51hzf26hl_C4MzeHkWiuWZ9to2Yo6s6o4.8ThfMJKrV62PymcY32baMtYZP74Vg.36aqlFMCVC63_EzPa.55tbHsttd |
|||
| .hsforms.com/ | 1970-01-21 17:41:46 |
Name: __cf_bm Value: AExEqGajA82RwO4oWN_VFlKCm6QP3tiwWG2Xsd.eFk8-1791704299.9629016-1.0.1.1-77wofKidJPGLkTuox43hY_cwk3IJ7p6oblFImTzc3Bsr6SQdU2lF4Cum_sE3f9CyjkM1nbeOglUD7zTiwwAFhDdJRCZe7.K28kXHGmTa.KhL1uZdYw1dtqcn502rx8Yt |
14 Console Messages
A page may trigger messages to the console to be logged. These are often error messages about being unable to load a resource or execute a piece of JavaScript. Sometimes they also provide insight into the technology behind a website.
| Source | Level | URL Text |
|---|
Indicators
This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.
14e1-180-254-64-204.ngrok.io
6403-180-254-64-204.ngrok.io
ajax.googleapis.com
api-na1.hubapi.com
aplo-evnt.com
assets.apollo.io
barnstablemassage.com
cdn.jsdelivr.net
cdn.shopify.com
cdnjs.cloudflare.com
code.jquery.com
connect.facebook.net
e9e1-180-254-64-204.ngrok.io
fonts.googleapis.com
fonts.gstatic.com
forms-na2.hscollectedforms.net
forms-na2.hsforms.com
gen.blackmolesamp.com
googlesignintest.loca.lt
js-na2.hs-analytics.net
js-na2.hs-banner.com
js-na2.hs-scripts.com
js-na2.hscollectedforms.net
meubelkayumurah.pics
outerbloom.com
shop.app
static.cloudflareinsights.com
track-na2.hubspot.com
ufo-bass.com
14e1-180-254-64-204.ngrok.io
6403-180-254-64-204.ngrok.io
e9e1-180-254-64-204.ngrok.io
outerbloom.com
104.17.24.14
104.18.80.204
142.251.110.94
172.67.157.114
178.128.116.123
188.114.96.3
188.114.97.3
193.34.76.44
2600:1901:0:658b::
2606:4700:10::ac42:8c49
2606:4700:4404::ac40:9310
2606:4700::6810:344e
2606:4700::6810:5049
2606:4700::6810:6dfe
2606:4700::6810:8dd1
2606:4700::6810:a0a8
2606:4700::6811:5cbb
2606:4700::6811:d005
2620:127:f00e:ff00::
2a00:1450:4001:c15::5f
2a00:1450:4001:c25::5f
2a04:4e42::411
2a06:98c1:3121::3
57.144.244.128
04d05978fdb111358073ab0524e5c1fafc0826615c206987618416b8bd8a4747
08c4fd72f9d96a7aa554510dff2c293973b1b092dff1b9b282bce9111b50ef41
2f589f98f1d5e06aafda996c17e4fe4b30e3736488a7b06600468cc542d19206
33557a376cac63af7343cef854a9d16501125fa1ffa251ca2990aa7cd10a4a1a
44136fa355b3678a1146ad16f7e8649e94fb4fc21fe77e8310c060f61caaff8a
45c6a51457cd1a536fcbf11d51ecdc225daf9635073cf6bc95381f57e87f6f46
472f66db8eace29dad29df703093912050be81343c2d37f579d4fb8f57100993
4b77eae349a8cbcea7133cf3640a64ebf1f69d54d8f6469d7be6fdc188ca4ca4
4cbce34f248f026b0d6456ff7832f48c94801feeea4bfa93e10f32a413ada863
4cf354bda9cb6678d7380e9c6687c1aa49b707c3d7121d7b71fe9ad7744d0752
53023fcf20b2a4a7c291b84569d835447d77f82adf87dba28861c549a3bee4f0
56f89e3c300aa936795b49cde889c002f0ea33c059f1371191b62bcb45e66031
57daad71b6979d335e5b6be88a94d73180fff8837b523e2035bcc2305644636e
582306c711e00c137fca729dc81e9b53e819fc7266808c4ec52eb8d684c85d97
668b046d12db350ccba6728890476b3efee53b2f42dbb84743e5e9f1ae0cc404
6adc3d4c1056996e4e8b765a62604c78b1f867cceb3b15d0b9bedb7c4857f992
6c802ea59c7231a75fec084e082ae62d6ad9aae2c973b5e0258642fd8f6bd6c1
7300a52a9e2aeecb3d345f23931912cb6495e6c807757c0ceba20607f6210b76
7808605ddd1f0eaa454aa444293d2f0260943e51e53838fca46506e6a69fe521
7c00351bfaec8d01035650badaa497aa4372e22ed9c46dcb69a810a4a36c36ba
7ec3bc2fb686c7902b68efe2f152a0f4348a732111d21c7a706c2f02570eb8a0
86528b9b3691944f120890b52b0f33a146d4f01c40fbc911de0b1eb8a7cc8f10
8df67312dca957f9d2af60825abae16a7a0e5dcb262a7694f4669b1be3649c3e
90263878a5eb73fcd9bb814e4c06545ba592eb48e54752cc8273335df8a63a7c
9528ca634fecad433d044ddd3e6f9ce1f068d5d932dafdbb19d8e6daea1968bd
954296e3d5b98a81ad7bc7e61ad992063b1a53c14f6f1f9d7d8dd696f2dca25a
977160bf9795324313e5daacf36be228ca2fc228a5d2dab191b6b06128783431
9c35cf87e4848a46e097f7223c011b0662b09a57d0b9d8d5be23d3678ba67ea3
a0fe8723dcf55da64d06b25446d0a8513e52527c45afcb37073465f9c6f352af
a12d5d6e9d5838478d7a86456aa9ab32a5f6715fe523ce91ca17b51d17eefc06
a2fe82406659ad9ab5fc997e99f26dc63614f3f6fc474a1a8a2483e5248b8800
aba0c13471d938833b60c46873e8c277e4953a194dd647158a1ac9777391b1dd
acbccb1e537481aaa809adb707a7287b2c47a072e2e3231990cc1d692aabf454
b5ce1b7d83a0d4f6c1c01377dbca6e840d6518cc108c552df37aa50274173db6
bbe0f49659faf4bcf2b84c4828943d869699ce8943fa3b17daaa648517fb7124
c541ef06327885a8415bca8df6071e14189b4855336def4f36db54bde8484f36
cda4a81c187015d95ed2c71f1841540b08203cdec5fa2a7d5d1825a3c2166f8c
d66dd0f2f24c4343661a5396e1ba76782fe651f7d422209eded956ebf90900fc
dc111a70984a9eda00752b06277113029ef288f1125c31eff2477413e15e8aa4
df2de6a62c309a5ca69104120b2dc3e00a5cbf725225b0d66e5a9a089c7a162b
e24435f282b201cca444a61e36e9c9708c32ed61f982da7026707b922b8b6751
e4222715b556e7d99622c83e620d2f8e090047e56adb07923047f95828d561f2
f2c08717584505bc70fbc66ffaad6816d2d72c28d59fa67a84ca46a0e709d07c
f7244fff610595b944f76bf3080d74e3af42b5dd234f8f079e698cc39ac966b0
f7f6a5894f1d19ddad6fa392b2ece2c5e578cbf7da4ea805b6885eb6985b6e3d
fb7b366bd65fb747ebc7d6e2af9d8a25b056c27c4551db320fe68799ca43dc91
fefb6a63e5224068802e435b623d7e318e9a1ac54541770460c655b2fe3008d7